The Cyber Toolchain — issue 082, September 22, 2026
THE CYBER TOOLCHAIN
NO. 082
Tail
THE DAILY RELEASE FIREHOSE
PUBLISHED SEPTEMBER 22, 2026 · EVERY DAY
EDITIONStail|grep|head|ls|diff|uniq
The daily firehose — everything the toolchain shipped today, already filtered.
We read every release from the 1309 tools on our watchlist at the source — GitHub and GitLab release notes, vendor release pages and changelogs, project blogs and feeds, vendor press releases, and the source code behind the tag. Bug-fix-only releases and non-product newsroom noise are dropped; what's left is summarized down to the new capability, how to try it, and any screenshots or videos the release itself published. Every entry links to the sources it was built from.
READ AS
Focus:What features shipped and what problems they solve, plus launches, packaging and where the market is moving.
Leaves out:Command-line flags, API-only deltas, usage examples, and releases that are only refinements.
Focus:New security controls, new APIs, and product improvements you can put to work, plus anything an upgrade breaks.
Leaves out:Launch and marketing news, governance, pricing, and documentation changes with no operational effect.
Focus:Dashboards, reporting, and anything you can quantify: metrics, coverage, risk scores, compliance impact, vendor moves.
Leaves out:Settings, flags, API and command-line detail, library bumps, and minor releases with no reporting or posture angle.
Focus:API, SDK and MCP changes, new libraries, breaking changes in what you import, and cyber tooling.
Leaves out:Governance, SOC operations, and vendor launches with no developer surface.
AMOUNT
DETAIL
ORDER
This issue came out before editions were ranked, so it shows the Standard edition in issue order.
What stands out across today's releases, grouped by what it lets you do. Every tool named links to its entry below.
Three unrelated things stand out. Falco 0.45.0 can match raw bytes in rule conditions, so detections stop depending on printable-string assumptions, and adds GPUGPUA graphics processing unit, a processor that performs many calculations in parallel. AI workloads use GPUs to speed up model training and inference. resource hijacking rules. NodeZero's pentests now follow footholds beyond the original scope through tunnels and Azure Run Command. StackHawk re-authenticates mid-scan, so a dropped session no longer silently hollows out an active DASTDASTDynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces. run.
detect
Write rules against bytes that never render as text, and catch GPU theft
Falco 0.45.0 matches and emits raw bytes in conditions and output, which is what you need for obfuscated payloads, binary protocol framing and non-UTF8 argv that string comparison quietly misses; new rules cover GPU resource hijacking, a real cost in shared AI infrastructure. Tetragon's matchUserCallers selector filters uprobe events by the user-space callstack, so a hook on a common library function fires only when the interesting caller is the one reaching it.
Stop a web scan from reporting clean because the session died halfway through
HawkScan 6.5.0 re-authenticates mid-scan when a session drops, closing the classic DAST failure where the second half of an authenticated crawl runs as an anonymous user and finds nothing; a rescan fix also stops legitimate headers being stripped from replayed requests. CrowdSec built AppSecAppSecApplication security: the practice of finding and fixing vulnerabilities in software during design, development, and testing. Cyber tools build on AppSec workflows to shift vulnerability detection earlier in the development lifecycle. into a full WAFWAFA reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. with ModSecurityModSecurityAn open-source web application firewall engine, maintained by the OWASP community, that inspects HTTP traffic against rule sets to block malicious requests before they reach an application. rule import and OWASP CRSOWASP CRSA free, community-maintained ruleset for ModSecurity and compatible WAFs that detects common web attacks like SQLi and XSS, giving cyber tools a ready-made detection baseline without writing rules from scratch. collections, plus alpha bot detection using proof-of-work challenges and device fingerprinting.
See which SaaS apps and AI agents your people actually signed up for
JumpCloud's SaaS ManagementSaaS ManagementA category of software that tracks, governs, and optimises an organisation's portfolio of SaaS subscriptions, covering spend, access, and licence utilisation from a single control plane. discovers shadow IT and adds a Windows Device Patch Report with CSV export, so the unsanctioned-app conversation starts from a list rather than an expense report. Okta's agent platform pairs shadow AI discovery with runtime enforcement and ephemeral credentialing — the point being that agents currently run on long-lived human credentials nobody inventories.
Three unrelated things stand out today: Google SecOpsSecOpsThe practice of merging security and IT operations teams so that threat detection, response, and infrastructure management share the same workflows, giving cyber tools a single pipeline from alert to remediation. can put AI triage and investigation agents inside playbooks, Falco can match raw bytes and flag GPUGPUA graphics processing unit, a processor that performs many calculations in parallel. AI workloads use GPUs to speed up model training and inference. resource hijacking, and code-oss can sandbox agent terminals at the OS boundary.
respond
Put AI triage and investigation inside the playbook instead of beside it
Agentic Automation embeds Triage and Investigation Agent steps directly in SecOps playbooks. That turns AI help from a separate analyst prompt into a repeatable case workflow, so enrichment and first-pass investigation can run where handoffs and approvals already live.
Catch lower-level runtime behavior that text rules miss
Raw byte matching lets Falco rules inspect data that does not survive cleanly as strings, while new GPU resource hijacking rules cover a resource-abuse path that is increasingly relevant on AI and compute nodes. Teams can express detections closer to what the kernel actually saw instead of relying on lossy text matching.
Run coding agents with file and network boundaries
OS-level agent terminal sandboxingsandboxingRunning code inside a restricted environment that limits what it can access or change. The isolation reduces the impact of mistakes or untrusted code, depending on the sandbox's controls. adds granular file-system and network controls around agent execution. That gives teams a way to let agents operate in developer workflows without handing them the same ambient host access as the user shell.
Find unmanaged SaaS and exported credentials before they become exceptions
JumpCloud added SaaS ManagementSaaS ManagementA category of software that tracks, governs, and optimises an organisation's portfolio of SaaS subscriptions, covering spend, access, and licence utilisation from a single control plane. for shadow-IT discovery and app governance, GitHub added Enterprise credential inventory export, and StepSecurity extended Apps & PATsPATsA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it. inventory to GitHub Enterprise Server. The common outcome is fewer spreadsheet-driven access hunts: teams can see unsanctioned apps, credentials, apps, and PATs from the systems that issue them.
Pentest reporting for consultancies that never put a client
Dradis Pro v5.4 adds QA states to gate client deliverables, an in-editor Roslin AI drafting tool for Content Blocks, new Webhook lifecycle events, dropdown-enforced List fields, and expanded custom field support in the Jira and DevOps integrations.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
5 FEATURES0 OF 5 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
QA states on Evidence gate report exportsnew70how completely this was documenteddepth30/40specificity20/30actionability20/3070 / 100
Adds QA states to Evidence so teams can track review status and gate client-facing deliverables — Excel and Word exports now only include Evidence marked as published.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ In practice, a reviewer opens a piece of Evidence, sets its QA state to Published from the Evidence view, and only published items appear in the subsequent Word or Excel export.
Use QA states to gate Evidence out of client deliverables — only published Evidence appears in Excel and Word exports.
📍In Dradis Pro, open a piece of Evidence, then set its QA state from the Evidence view (e.g. mark it Published once reviewed). Repeat for each Evidence item before exporting your Word or Excel report.
Mark reviewed Evidence as published so only approved findings appear in client-facing Excel and Word exports.
📍1. Open a piece of Evidence in your project.
2. Locate the QA state control in the Evidence view.
3. Set the state to Published once review is complete.
4. Export the report — only Evidence marked as published will appear in the Excel or Word output.
Mark Evidence as reviewed before export to ensure only published Evidence reaches the client Word or Excel report.
📍In a project, open a piece of Evidence › locate the QA state selector in the Evidence view › set the state to Published before generating a Word or Excel export.
Gate client deliverables by marking each piece of Evidence with a QA state before export, ensuring only reviewed Evidence appears in Word and Excel reports.
📍In a project, open a piece of Evidence, then set its QA state to Published from the Evidence view. When you export the report (Excel or Word), only Evidence marked as published will be included.
Gate client deliverables by marking Evidence through QA review before export — only published Evidence appears in Word and Excel reports.
📍In a project, open a piece of Evidence, then use the QA state selector in the Evidence view to mark it as reviewed/published before generating your Word or Excel export.
Mark Evidence as reviewed before export so only published Evidence appears in client-facing Word and Excel deliverables.
📍In Dradis, open a piece of Evidence › locate the QA state control in the Evidence view › set the state to Published before generating the report.
After completing review of a piece of evidence, mark it as published so it is included in the Word or Excel report export — unpublished evidence is now excluded automatically.
📍In the project, open a piece of Evidence › set its QA state to Published from the Evidence view › generate the Word or Excel export — only published Evidence will appear in the deliverable.
Track Evidence review status before sending a report to a client, keeping unreviewed material out of exported deliverables.
📍In a project, open a piece of Evidence, then set its QA state from the Evidence view. Only Evidence marked as published will appear in Excel and Word exports.
Roslin AI drafting in Content Blocksnew60how completely this was documenteddepth25/40specificity20/30actionability15/3060 / 100
Adds a Roslin agent tab to Content Blocks to draft report sections (executive summaries, methodology, scope notes) from the full project content including Issues and Evidence, without leaving the block. A user opens a Content Block, selects the Roslin tab, and prompts it to draft a section based on the project's findings.
Draft an executive summary or methodology section using Roslin directly inside a Content Block, drawing on the full project context.
📍Open a Content Block in your project, navigate to the Roslin tab, and ask it to draft the section — for example: 'Draft an executive summary based on all Issues and Evidence in this project.'
Draft a recurring report section (e.g. executive summary) from full project content without leaving the Content Block.
📍1. Open a Content Block in your project.
2. Select the Roslin tab.
3. Ask Roslin to draft the section — for example: 'Draft an executive summary based on this project'.
4. Roslin responds using the full project content, including Issues and Evidence.
Draft an executive summary for a Content Block using the full project context — Issues and Evidence included — without leaving the block.
📍Open a Content Block › select the Roslin tab › type a prompt such as 'Draft an executive summary based on the findings in this project' › review and insert the generated text.
Draft an executive summary for a Content Block using Roslin, drawing on all Issues and Evidence already in the project rather than rewriting from scratch.
📍Open a Content Block, navigate to the Roslin tab, and ask Roslin to draft the section (e.g. 'Draft an executive summary based on all Issues and Evidence in this project').
Draft a recurring report section such as an executive summary directly from all project findings without leaving the Content Block.
📍Open a Content Block, navigate to the Roslin tab, and prompt Roslin to draft the section — it reads from the full set of project Issues and Evidence to produce the content.
Draft an executive summary or methodology section for a recurring Content Block using the full project context without leaving the block.
📍In Dradis, open a Content Block › select the Roslin tab › type a prompt such as 'Draft an executive summary based on all Issues and Evidence in this project' › review and save the generated content.
Draft an executive summary for a recurring Content Block without leaving Dradis, using the full project context (Issues and Evidence) as source material.
📍Open a Content Block › click the Roslin tab › type a prompt such as 'Draft an executive summary based on the issues and evidence in this project' › review and accept the drafted section.
Draft a recurring report section such as an executive summary or methodology note without leaving the Content Block.
📍Open a Content Block, navigate to the Roslin tab, and ask Roslin to draft the section — it draws on the full project content including Issues and Evidence.
Webhook events for Evidence, Node, and Notenew55how completely this was documenteddepth20/40specificity25/30actionability10/3055 / 100
Adds Evidence, Node, and NoteCRUDCRUDThe four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. events to Webhooks, enabling external systems to react to evidence lifecycle changes.
Expanded custom field support in Jira and DevOps integrationsimproved55how completely this was documenteddepth20/40specificity25/30actionability10/3055 / 100
Adds support for float custom fields and multiselect custom fields when sending issues to Jira, and adds support for numeric (integer and double) Work Item fields and required fields in the DevOps integration.
List fields rendered as dropdownsimproved50how completely this was documenteddepth20/40specificity20/30actionability10/3050 / 100
Renders List fields as selects (dropdowns) when editing existing Issues, Evidence, and Content Blocks, enforcing consistent field values across a project.
Dradis Pro v5.4 adds QA states to Evidence, Roslin AI drafting for Content Blocks, List fields as dropdowns, and Webhook CRUDCRUDThe four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. events.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
After completing review of a piece of evidence, mark it as published so it is included in the Word or Excel report export — unpublished evidence is now excluded automatically.
📍In the project, open a piece of Evidence › set its QA state to Published from the Evidence view › generate the Word or Excel export — only published Evidence will appear in the deliverable.
Draft an executive summary for a recurring Content Block without leaving Dradis, using the full project context (Issues and Evidence) as source material.
📍Open a Content Block › click the Roslin tab › type a prompt such as 'Draft an executive summary based on the issues and evidence in this project' › review and accept the drafted section.
Adds Evidence, Node, and Note CRUD events to Webhooks, enabling external systems to react to evidence lifecycle changes.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds QA states to Evidence so teams can track review status and gate client-facing deliverables — Excel and Word exports now only include published Evidence.
Adds a Roslin agent tab to Content Blocks to draft report sections (executive summaries, methodology, scope notes) from the full project content including Issues and Evidence.
Renders List fields as selects (dropdowns) when editing existing Issues, Evidence, and Content Blocks, enforcing consistent field values across a project.
Adds support for numeric (integer and double) Work Item fields and required fields in the DevOps integration.
+1 moreshow less
Adds support for float custom fields and multiselect custom fields when sending issues to Jira.
Adds Evidence, Node, and Note CRUD events to Webhooks, enabling external systems to react to evidence lifecycle changes.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds QA states to Evidence so teams can track review status and gate client-facing deliverables — Excel and Word exports now only include published Evidence.
Adds a Roslin agent tab to Content Blocks to draft report sections (executive summaries, methodology, scope notes) from the full project content including Issues and Evidence.
Renders List fields as selects (dropdowns) when editing existing Issues, Evidence, and Content Blocks, enforcing consistent field values across a project.
Veracode is a cloud-based application security platform that performs static, dynamic, and software composition analysis to identify vulnerabilities in code.
Veracode expanded platform integrations and scanning accuracy this window, adding Jira 11 support to its Jira Server integration, refining Python scanner flaw matching against a baseline scan, and redesigning its EASMEASMExternal Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do. interface.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
3 FEATURES1 OF 3 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Jira Server integration updated for Jira 11improved60how completely this was documenteddepth20/40specificity25/30actionability15/3060 / 100
Veracode Integration for Jira Server v5.0.2 adds support for Jira 11, including Java 21 and platform compatibility with Jira 11.3.10.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Python scanner flaw matching baselinebreaking50how completely this was documenteddepth25/40specificity15/30actionability10/3050 / 100
The enhanced Python scanner now uses each application's initial scan baseline for consistent flaw matching across subsequent scans. Customers who transitioned to the enhanced Python scanner on July 22, 2026 may find previously identified flaws no longer match historical findings, and previously applied mitigations may need to be reapplied.
Redesigned EASM UIimproved10how completely this was documenteddepth5/40specificity5/30actionability0/3010 / 100
Veracode shipped a redesigned UI for its external attack surfaceattack surfaceThe exposed systems, interfaces and access points an attacker could try to use. It includes internet-facing services as well as identities, software and other reachable resources. management (EASM) capability.
Customers who transitioned to the enhanced Python scanner on July 22, 2026 may find that previously identified flaws no longer match historical findings and previously applied mitigations may need to be reapplied.
Veracode adds Jira 11 support, a redesigned EASMEASMExternal Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do. UI, and improved Python scanner flaw matching.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Veracode Integration for Jira Server v5.0.2 adds support for Jira 11, including Java 21 and platform compatibility with Jira 11.3.10.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Enhanced Python scanner now uses each application's initial scan baseline for consistent flaw matching across subsequent scans.
Veracode Integration for Jira Server v5.0.2 adds support for Jira 11, including Java 21 and platform compatibility with Jira 11.3.10.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
1 more in Everything
└──▷ BREAKING ON UPGRADE
!Customers who transitioned to the enhanced Python scanner on July 22, 2026 may find that previously identified flaws no longer match historical findings and previously applied mitigations may need to be reapplied.
HawkScan 6.5.0 adds mid-scan session re-authentication to catch dropped sessions during active scans, a one-line versioned CLI installer, and org-wide secret resolution, alongside a rescan fix that stops legitimate headers from being stripped from replayed requests.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
StackHawk is an application security tool built for developers. Automated scanning for the entire dev pipeline combined with continuous documentation and remediation.
HawkScan 6.5.0 adds mid-scan session re-authentication to catch dropped sessions during active scans, a one-line versioned CLI installer, and org-wide secret resolution, alongside a rescan fix that stops legitimate headers from being stripped from replayed requests.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
5 FEATURES0 OF 5 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Mid-scan session verificationnew91how completely this was documenteddepth35/40specificity28/30actionability28/3091 / 100
Adds an opt-in sessionVerification block under app.authentication in stackhawk.yml with pollFrequency (default 15), activeScanPollFrequency (default 5), maxUnauthenticatedRequestPercent (default 5), and disabled fields to actively poll authentication.testPath and re-authenticate sessions mid-scan rather than relying on passive response indicators.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Supports both HTTP testPath and gRPCgRPCAn open-source remote procedure call framework from Google that uses HTTP/2 and Protocol Buffers to let services call each other's functions across a network, giving tools low-latency, strongly typed inter-process communication.testPath.grpcTestMethod styles, with testPath.type values HEADER and BODY honored, and surfaces a coverage warning at scan completion if too many mid-scan checks fail unauthenticated, catching scans that silently ran as an anonymous user; disabled: true turns off active checks while still requiring an indicator-based check.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Enable mid-scan session re-authentication so HawkScan detects and recovers from dropped sessions during active attack phases, with a warning if more than 10% of checks are unauthenticated.
Enable mid-scan session re-authentication so unauthenticated drift during an active attack scan is caught and corrected automatically, with tighter polling during active scanning.
— Full config block, fields, defaults and behavior all namedsnapshot-20260922
0200
One-line HawkScan CLI installernew88how completely this was documenteddepth30/40specificity28/30actionability30/3088 / 100
Adds a one-line installer script, curl -sSf https://download.stackhawk.com/hawk/install.sh | sh, that detects OS and architecture and verifies SHA-256SHA-256A cryptographic hash function that turns data into a fixed 256-bit fingerprint. It is used to check integrity; hashing does not encrypt the original data. against the published manifest. Supports HAWK_INSTALL_VERSION to pin the CLI version (recommended for reproducible CI pipelines) and HAWK_INSTALL_DIR to control install location, which defaults to ~/.hawk/bin.
Pin the hawk CLI to a specific version in CI so your pipeline stays reproducible and does not break when a new release drops.
$ HAWK_INSTALL_VERSION=6.5.0 HAWK_INSTALL_DIR=/usr/local/bin curl -sSf https://download.stackhawk.com/hawk/install.sh | sh
Pin the HawkScan CLI to a specific version in CI for a reproducible pipeline, installing to a custom directory.
$ HAWK_INSTALL_VERSION=6.5.0 HAWK_INSTALL_DIR=/opt/hawk/bin curl -sSf https://download.stackhawk.com/hawk/install.sh | sh
— Runnable install command with named env vars and defaultssnapshot-20260922
thinner coverage below
0300
Headers no longer stripped on rescanimproved55how completely this was documenteddepth25/40specificity20/30actionability10/3055 / 100
Entity and transport headers — Content-Type, Content-Length, Accept, Accept-Encoding, Host, User-Agent, Referer — are no longer stripped from replayed requests during rescans, preventing spurious 415 responses from masking unresolved findings.
— Names headers and effect but no action step for readerproduct docs
0400
Organization-level secret resolutionnew50how completely this was documenteddepth25/40specificity15/30actionability10/3050 / 100
Adds organization-level secret resolution so ${VARIABLE} references in scan configuration now resolve against org-shared secrets, not only per-user secrets; personal secrets still take precedence, and unresolved names now emit a named warning instead of silently resolving to an empty value.
— Explains mechanism but no concrete config path shownsnapshot-20260922
0500
CLI minimum-version enforcement messagingimproved45how completely this was documenteddepth25/40specificity10/30actionability10/3045 / 100
Adds clear error messaging when the HawkScan CLI version is below the platform-enforced minimum, reporting the minimum supported version and upgrade location and exiting non-zero instead of emitting a generic HTTP error; deprecated-but-not-blocked versions now log an advisory once per scan rather than on every platform call.
— Describes behavior change but no exact command or codesnapshot-20260922
HawkScan 6.5.0 adds mid-scan session verification, org-wide secrets, and a one-line CLI installer with version pinning.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Pin the hawk CLI to a specific version in CI so your pipeline stays reproducible and does not break when a new release drops.
$ HAWK_INSTALL_VERSION=6.5.0 HAWK_INSTALL_DIR=/usr/local/bin curl -sSf https://download.stackhawk.com/hawk/install.sh | sh
Enable mid-scan session re-authentication so unauthenticated drift during an active attack scan is caught and corrected automatically, with tighter polling during active scanning.
Adds app.authentication.sessionVerification config block to re-check and re-authenticate sessions mid-scan by polling authentication.testPath, with tunable pollFrequency (default 15), activeScanPollFrequency (default 5), and maxUnauthenticatedRequestPercent (default 5); a scan that spent too much time logged out now finishes with a coverage warning instead of a silently thin result.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds disabled: true field inside app.authentication.sessionVerification to explicitly turn off session verification while still requiring an indicator-based check.
Adds a one-line installer script at curl -sSf https://download.stackhawk.com/hawk/install.sh | sh that detects OS and architecture, verifies SHA-256SHA-256A cryptographic hash function that turns data into a fixed 256-bit fingerprint. It is used to check integrity; hashing does not encrypt the original data. against the published manifest, and supports HAWK_INSTALL_VERSION and HAWK_INSTALL_DIR environment variables (default install location ~/.hawk/bin).
Adds HAWK_INSTALL_VERSION environment variable to pin the hawk CLI version during install — recommended for reproducible CI pipelines.
Adds HAWK_INSTALL_DIR environment variable to control where the hawk binary is installed (default ~/.hawk/bin).
+2 moreshow less
Adds organization-level secret resolution so ${VARIABLE} references in scan configuration now resolve against org-shared secrets, not only per-user secrets; personal secrets still take precedence, and unresolved names now emit a named warning instead of silently resolving to an empty value.
Adds clear error messaging when the HawkScan CLI version is below the platform-enforced minimum, reporting the minimum supported version, upgrade location, and exiting non-zero instead of emitting a generic HTTP error; deprecated-but-not-blocked versions log an advisory once per scan rather than on every platform call.
Adds app.authentication.sessionVerification config block to re-check and re-authenticate sessions mid-scan by polling authentication.testPath, with tunable pollFrequency (default 15), activeScanPollFrequency (default 5), and maxUnauthenticatedRequestPercent (default 5); a scan that spent too much time logged out now finishes with a coverage warning instead of a silently thin result.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds disabled: true field inside app.authentication.sessionVerification to explicitly turn off session verification while still requiring an indicator-based check.
Adds a one-line installer script at curl -sSf https://download.stackhawk.com/hawk/install.sh | sh that detects OS and architecture, verifies SHA-256SHA-256A cryptographic hash function that turns data into a fixed 256-bit fingerprint. It is used to check integrity; hashing does not encrypt the original data. against the published manifest, and supports HAWK_INSTALL_VERSION and HAWK_INSTALL_DIR environment variables (default install location ~/.hawk/bin).
Adds HAWK_INSTALL_VERSION environment variable to pin the hawk CLI version during install — recommended for reproducible CI pipelines.
Adds HAWK_INSTALL_DIR environment variable to control where the hawk binary is installed (default ~/.hawk/bin).
GitHub shipped a generally-available refresh of the repository pull requests page with advanced search and bulk actions, added a full credential inventory export for Enterprise, and rolled out the Grok 4.7 model in Copilot.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Join the world's most widely adopted, AI-powered developer platform where millions of developers, businesses, and the largest open source community build software that advances humanity.
GitHub shipped a generally-available refresh of the repository pull requests page with advanced search and bulk actions, added a full credential inventory export for Enterprise, and rolled out the Grok 4.7 model in Copilot.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
3 FEATURES2 OF 3 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0101
Enterprise credential inventory exportnew87how completely this was documenteddepth35/40specificity30/30actionability22/3087 / 100
GitHub Enterprise adds a new View enterprise credentials fine-grained permission granting members access to the credential inventory alongside enterprise owners, plus new paginated REST APIREST APIA web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. endpoints to programmatically retrieve the complete inventory.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ An Export CSV option in enterprise Settings -> Authentication Security -> Credentials downloads the full inventory, which includes owners, scopes and permissions, creation and expiration dates, last-used dates, and target organizations or repositories; it can be filtered by user, app, credential type, or organization, and covers SSH keys, classic and fine-grained personal access tokenspersonal access tokensA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it., OAuth App access tokensaccess tokensA credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions., and GitHub App user-to-server and installation tokens.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Export a one-off CSV snapshot of all enterprise credentials for offline review or audit when you don't need automation.
📍In your enterprise, go to Settings -> Authentication Security -> Credentials and click Export CSV next to the Overview section.
Refreshed pull requests page generally availablenew85how completely this was documenteddepth35/40specificity25/30actionability25/3085 / 100
The pull requests page now supports advanced search with AND and OR keywords and nested searches, and bulk actions to close, label, or change milestones on one or more pull requests at once. A collapsible sidebar gives quick access to common filters like Authored by me and Involves me and can be collapsed to expand the list view; a compact presentation mode fits more pull requests on the page. The list now surfaces status check counts, stack indicators, unread-update indicators, milestones, linked issues, and author badges directly, clicking a review status filters the list by that status, and full profile names are shown when enabled for an enterprise.
Narrow a busy repository's PR list to open, approved PRs that still need a specific team's attention — combining OR and AND in one query.
📍In the repository pull requests page, enter into the search bar: is:open review:approved AND (involves:@my-org/security-team OR involves:@my-org/platform-team)
Quickly close or re-label a batch of stale PRs without opening each one individually.
📍In the repository pull requests page, check the checkboxes next to the target pull requests, then open the Label or Close bulk-action menu that appears at the top of the list.
Grok 4.7 model in Copilotnew65how completely this was documenteddepth25/40specificity20/30actionability20/3065 / 100
The Grok 4.7 reasoning model is now available in GitHub Copilot across VS Code, JetBrains, Xcode, Eclipse, CLI, and the cloud agent. Copilot Enterprise and Business administrators manage access via the model policy in Copilot settings, where new models are auto-enabled under the global default unless explicitly disabled.
Restrict or permit Grok 4.7 for your organisation by toggling its model policy in Copilot settings.
📍In GitHub, go to your organisation's Settings › Copilot › Policies, find Grok 4.7 under model enablement, and set it to Enabled or Disabled as required.
GitHub's refreshed pull requests page is now GA, with AND/OR advanced search, bulk actions, and a collapsible sidebar.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
Narrow a busy repository's PR list to open, approved PRs that still need a specific team's attention — combining OR and AND in one query.
📍In the repository pull requests page, enter into the search bar: is:open review:approved AND (involves:@my-org/security-team OR involves:@my-org/platform-team)
Quickly close or re-label a batch of stale PRs without opening each one individually.
📍In the repository pull requests page, check the checkboxes next to the target pull requests, then open the Label or Close bulk-action menu that appears at the top of the list.
Advanced search on the pull requests page now supports AND and OR keywords as well as nested searches.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Bulk actions let you close, label, or change milestones on one or more pull requests at once.
Collapsible sidebar provides quick access to common filters such as Authored by me and Involves me, and can be collapsed to expand the list view.
Compact presentation mode fits more pull requests on the page.
Pull request list now surfaces status check counts, stack indicators, and unread-update indicators.
+3 moreshow less
Clicking a review status in the list filters pull requests by that status.
Milestones, linked issues, and author badges are now visible directly in the pull request list.
Full profile names are shown when enabled for an enterprise.
Advanced search on the pull requests page now supports AND and OR keywords as well as nested searches.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Bulk actions let you close, label, or change milestones on one or more pull requests at once.
Collapsible sidebar provides quick access to common filters such as Authored by me and Involves me, and can be collapsed to expand the list view.
Compact presentation mode fits more pull requests on the page.
Clicking a review status in the list filters pull requests by that status.
GitHub Enterprise gains a full credential inventory export — CSV from the UI or via new paginated REST APIREST APIA web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. endpoints.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
Export a one-off CSV snapshot of all enterprise credentials for offline review or audit when you don't need automation.
📍In your enterprise, go to Settings -> Authentication Security -> Credentials and click Export CSV next to the Overview section.
Adds a new View enterprise credentials fine-grained permission that grants members access to the enterprise credential inventory alongside enterprise owners.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds new paginated REST API endpoints to programmatically retrieve the complete enterprise credential inventory for reporting and automation.
Adds an Export CSV option in enterprise Settings -> Authentication Security -> Credentials to download the full credential inventory.
Surfaces credential metadata in the inventory including owners, scopes and permissions, creation and expiration dates, last-used dates, and target organizations or repositories.
Supports filtering the credential inventory by user, app, credential type, or organization.
+1 moreshow less
Covers SSH keys, classic and fine-grained personal access tokenspersonal access tokensA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it., OAuth App access tokensaccess tokensA credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions., and GitHub App user-to-server and installation tokens in the exported inventory.
Grok 4.7 reasoning model now available in GitHub Copilot across VS Code, JetBrains, Xcode, Eclipse, CLI, and cloud agent.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
Restrict or permit Grok 4.7 for your organisation by toggling its model policy in Copilot settings.
📍In GitHub, go to your organisation's Settings › Copilot › Policies, find Grok 4.7 under model enablement, and set it to Enabled or Disabled as required.
Copilot Enterprise and Business administrators can manage access to Grok 4.7 via the model policy in Copilot settings, with new models auto-enabled under the global default unless explicitly disabled.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
SonarQube is the independent AI code verification platform trusted by 7M+ developers & organizations to help build secure, reliable software with confidence.
SonarQube launched Hunter Agent, a new AI-driven verification layer that hunts for business-logic, access-control, and authentication flaws beyond the reach of static analysis and SCASCASoftware composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself., and wires the results straight into existing triage and compliance workflows.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
1 FEATURE1 OF 1 FEATUREmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0101
Hunter Agent AI vulnerability detectionnew73how completely this was documenteddepth32/40specificity26/30actionability15/3073 / 100
Hunter Agent is a new AI-driven verification layer that runs structured multi-stage playbooks to detect business-logic, broken access control, and authentication/session vulnerabilities — classes of flaw that static analysis and SCA miss.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Findings surface as standard SonarQube issues (with severity, file, and line) inside the existing triage, assignment, and tracking workflow, and are also summarized on a dedicated Hunter Agent page; it can be run manually or on a daily schedule against long-lived branches.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ It produces a reproducible, auditable evidence trail from detection through remediation, mapped to DORA, NIS2NIS2EU directive that expands mandatory cybersecurity requirements to more sectors and member states than its predecessor, giving cyber tools a compliance framework to map controls and reporting obligations against., PCI DSSPCI DSSThe Payment Card Industry Data Security Standard, security requirements for protecting payment account data. It covers organizations that store, process or transmit that data and relevant service providers. 4.0.1, HIPAAHIPAAA US federal law enacted in 1996 that sets privacy and security requirements for protected health information, giving cyber tools a compliance baseline to enforce or audit against., GDPRGDPREU regulation enacted in 2018 that governs how organizations collect, store, and process personal data of EU residents, giving cyber tools legal obligations around data handling and breach notification., EU CRAEU CRAEU Cyber Resilience Act, a European Union regulation requiring manufacturers and publishers of products with digital elements to meet mandatory cybersecurity standards before selling into the EU market., NYDFS, and FDA 21 CFR Part 11 requirements.
— Names mechanism, workflow integration, scheduling, and compliance mappings; no config/API surface given.launch-20260921-74341ed0
SonarQube Hunter Agent adds AI-driven detection of business logic, access control, and authentication flaws as standard issues.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds Hunter Agent, a new AI-driven verification layer that detects business-logic, broken access control, and authentication/session vulnerabilities through structured multi-stage playbooks — classes of flaw that static analysis and SCASCASoftware composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. miss.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Surfaces Hunter Agent findings as standard SonarQube issues (with severity, file, and line) in the existing triage, assignment, and tracking workflow, with results also summarized on a dedicated Hunter Agent page.
Supports running Hunter Agent manually or on a daily schedule against long-lived branches to suit different team cadences.
Produces a reproducible, auditable evidence trail from detection through triage and remediation, mapped to DORA, NIS2NIS2EU directive that expands mandatory cybersecurity requirements to more sectors and member states than its predecessor, giving cyber tools a compliance framework to map controls and reporting obligations against., PCI DSSPCI DSSThe Payment Card Industry Data Security Standard, security requirements for protecting payment account data. It covers organizations that store, process or transmit that data and relevant service providers. 4.0.1, HIPAAHIPAAA US federal law enacted in 1996 that sets privacy and security requirements for protected health information, giving cyber tools a compliance baseline to enforce or audit against., GDPRGDPREU regulation enacted in 2018 that governs how organizations collect, store, and process personal data of EU residents, giving cyber tools legal obligations around data handling and breach notification., EU CRAEU CRAEU Cyber Resilience Act, a European Union regulation requiring manufacturers and publishers of products with digital elements to meet mandatory cybersecurity standards before selling into the EU market., NYDFS, and FDA 21 CFR Part 11 requirements.
Pi Security triages vulnerability and bug-bounty reports with agentic AI, analyzes the organisation's code and cloud context and generates fixes for developers.
Pi Security launched an integration with Anthropic's Compliance API and introduced Sloane, an in-session agent that surfaces security context to developers as they write code.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
2 FEATURES0 OF 2 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Sloane in-session security agentnew45how completely this was documenteddepth20/40specificity15/30actionability10/3045 / 100
Sloane is Pi's agent running natively in the coding session, surfacing security context to developers as code is written rather than in post-review.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Pi Security integrates with Anthropic's Compliance API and delivers security context in-session via its Sloane agent.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Integrates with Anthropic's Compliance API to maintain a complete compliance record of security context delivered to developers.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Introduces Sloane, Pi's agent running natively in the coding session, to surface security context to developers as code is written rather than in post-review.
StepSecurity extended its Apps & PATsPATsA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it. inventory to GitHub Enterprise Server and added CC recipients, per-token-class schedules, and customizable email content to PATPATA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it. expiry reminders.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
StepSecurity hardens CI/CD pipelines by detecting and preventing supply chain attacks through runtime security monitoring and vulnerability detection.
StepSecurity extended its Apps & PATsPATsA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it. inventory to GitHub Enterprise Server and added CC recipients, per-token-class schedules, and customizable email content to PATPATA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it. expiry reminders.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
2 FEATURES0 OF 2 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
PAT reminder CC recipients, custom schedules and email contentimproved93how completely this was documenteddepth35/40specificity28/30actionability30/3093 / 100
PAT Governance reminders now support CC recipients so additional addresses (e.g.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ a security distribution list) are copied on every pre-expiry PAT reminder. Per-token-class reminder schedules add optional classic and fine-grained overrides that replace the shared default schedule (30, 7, 1 days before expiry) for one class. Per-token-class and per-reminder-band subject and body editors are prefilled with the default email and support placeholders for owner, token name, organization, days left, expiry date, and the management URL.
Route all PAT expiry reminders to a security team inbox in addition to the org notification address, and set a tighter fine-grained-only schedule.
📍In the StepSecurity console, go to Settings › Control Evaluation › Reminders & Automation (PAT Governance Controls). Under CC Recipients, add your security distribution list address. Under Reminder Schedule, enable the fine-grained override and set custom days (e.g. 14, 3, 1) to replace the shared 30/7/1-day default for fine-grained tokens only.
Customize the 1-day pre-expiry email body for classic tokens to include your internal rotation runbook URL.
📍In the StepSecurity console, go to Settings › Control Evaluation › Reminders & Automation (PAT Governance Controls). Select the classic token class and the 1 day reminder band, then edit the subject and body fields — use placeholders such as {{owner}}, {{token_name}}, {{organization}}, {{days_left}}, {{expiry_date}}, and {{management_url}} — and save. Fields left unchanged keep the built-in email.
Apps & PATs inventory for GitHub Enterprise Servernew45how completely this was documenteddepth20/40specificity15/30actionability10/3045 / 100
The Apps & PATs page now covers GitHub Enterprise Server organizations, inventorying installed GitHub Apps and fine-grained personal access tokenspersonal access tokensA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it. with permission, access scope, and status detail.
StepSecurity Apps & PATsPATsA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it. Inventory now available for GitHub Enterprise Server organizations.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
StepSecurity PATPATA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it. Governance now supports CC recipients and per-class, per-band custom email content for pre-expiry token reminders.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
Route all PAT expiry reminders to a security team inbox in addition to the org notification address, and set a tighter fine-grained-only schedule.
📍In the StepSecurity console, go to Settings › Control Evaluation › Reminders & Automation (PAT Governance Controls). Under CC Recipients, add your security distribution list address. Under Reminder Schedule, enable the fine-grained override and set custom days (e.g. 14, 3, 1) to replace the shared 30/7/1-day default for fine-grained tokens only.
Customize the 1-day pre-expiry email body for classic tokens to include your internal rotation runbook URL.
📍In the StepSecurity console, go to Settings › Control Evaluation › Reminders & Automation (PAT Governance Controls). Select the classic token class and the 1 day reminder band, then edit the subject and body fields — use placeholders such as {{owner}}, {{token_name}}, {{organization}}, {{days_left}}, {{expiry_date}}, and {{management_url}} — and save. Fields left unchanged keep the built-in email.
Adds CC recipient support so additional addresses (e.g.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ a security distribution list) are copied on every pre-expiry PAT reminder sent by the organization.
Adds per-token-class reminder schedules with optional classic and fine-grained overrides that replace the shared default schedule (30, 7, 1 days before expiry) for one class.
Adds per-token-class and per-reminder-band subject and body editors, prefilled with the default email, supporting placeholders for owner, token name, organization, days left, expiry date, and the management URL.
Adds CC recipient support so additional addresses (e.g.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ a security distribution list) are copied on every pre-expiry PAT reminder sent by the organization.
Adds per-token-class and per-reminder-band subject and body editors, prefilled with the default email, supporting placeholders for owner, token name, organization, days left, expiry date, and the management URL.
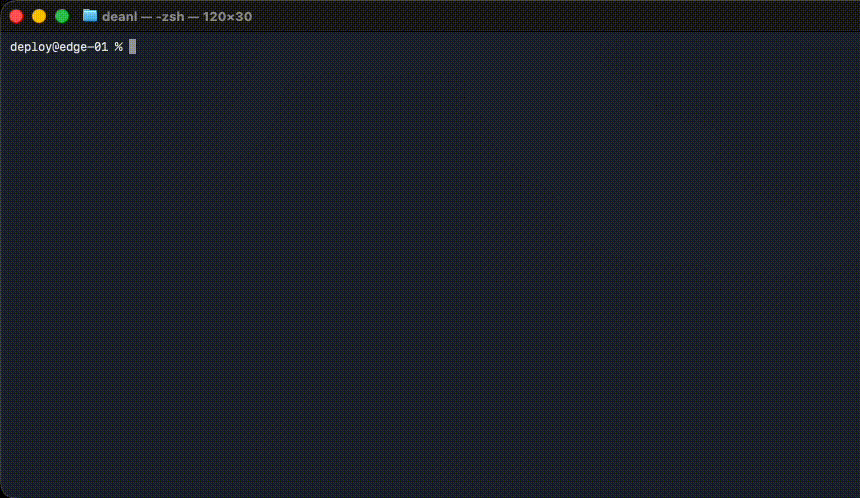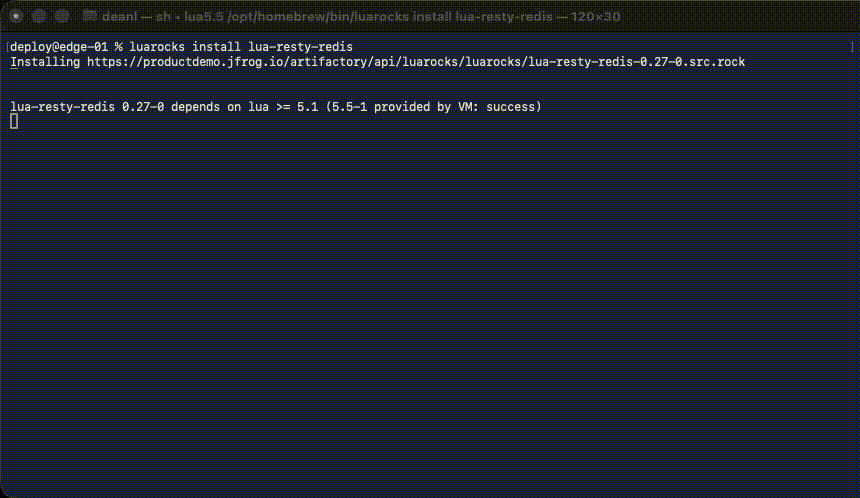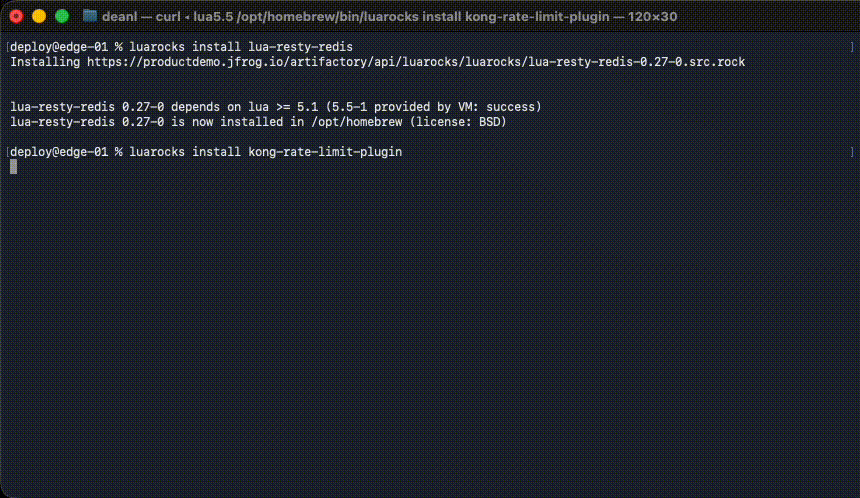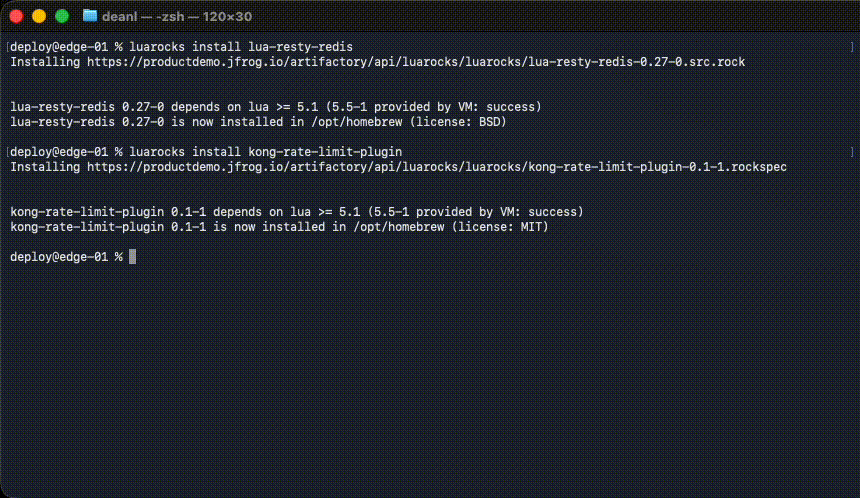
JFrog Artifactory adds native LuaRocksLuaRocksThe package manager for the Lua programming language, maintained by the LuaRocks project, used to distribute and install Lua modules so tools can pull in versioned dependencies without bundling them manually. repository support, letting teams host, proxy, and cache Lua packages and Kong plugins through local, remote, and virtual repositories.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
JFrog provides DevOps platform for software delivery, managing artifacts, dependencies, and continuous integration/deployment pipelines.
JFrog Artifactory adds native LuaRocksLuaRocksThe package manager for the Lua programming language, maintained by the LuaRocks project, used to distribute and install Lua modules so tools can pull in versioned dependencies without bundling them manually. repository support, letting teams host, proxy, and cache Lua packages and Kong plugins through local, remote, and virtual repositories.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
1 FEATURE0 OF 1 FEATUREmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
LuaRocks repository support in Artifactorynew75how completely this was documenteddepth32/40specificity25/30actionability18/3075 / 100
Artifactory adds LuaRocks as a native repository type, supporting local, remote, and virtual repository configurations for Lua packages.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Remote repositories proxy and cache the public luarocks.org registry, serving cached rocks on subsequent requests. Local repositories let CI jobs publish .rock files and host private rocks and Kong plugins so Kong nodes can install versioned plugins from a single internal endpoint, while a virtual repository unifies private and cached public rocks behind a single URL for the luarocks client.
JFrog Artifactory adds native LuaRocksLuaRocksThe package manager for the Lua programming language, maintained by the LuaRocks project, used to distribute and install Lua modules so tools can pull in versioned dependencies without bundling them manually. repository support for hosting, proxying, and caching Lua rocks.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds LuaRocks as a native repository type in JFrog Artifactory, supporting local, remote, and virtual repository configurations for Lua packages.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Supports proxying and caching the public luarocks.org registry through a remote repository, serving cached rocks on subsequent requests.
Enables hosting private rocks and Kong plugins in a local LuaRocks repository, allowing CI jobs to publish .rock files and Kong nodes to install versioned plugins from a single internal endpoint.
Provides a virtual LuaRocks repository that unifies private and cached public rocks behind a single URL for the luarocks client.
GitGuardian Detection Engine scans code repositories to identify and alert on exposed secrets, credentials, and sensitive data.
GitGuardian's Detection Engine 2.172 release substantially widens secret coverage, adding 10 new detectors, 2 new checkers, and 8 new secret analyzers, while also improving match recall across several existing detectors and retiring a deprecated Figma scope.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
5 FEATURES0 OF 5 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Expanded detection recall for Scaleway, Splunk, Salesforce, and generic detectorsimproved71how completely this was documenteddepth32/40specificity29/30actionability10/3071 / 100
The Scaleway Token detector now catches SCW_SECRET_KEY and SCALEWAY_SECRET_KEY assignments, including documents where the word scaleway is absent.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ The Splunk Authentication Token detector now also matches an optional Splunk host alongside the token. The Salesforce OAuth2OAuth2An open authorization framework (RFC 6749) that lets a service grant limited access to a user's resources on another service without exposing credentials, giving cyber tools a standard way to authenticate against third-party APIs. Keys detector now captures the Salesforce instance host and validates against that instance's OAuth token endpoint (production or sandbox), returning failed_to_check when no host is found. The Username Password detector now also matches Spanish, Portuguese, French, and Turkish username/password assignment keywords. The generic_high_entropy_secret and generic_encryption_key detectors now report secrets/keys located near a localhost mention. The generic_database_assignment_attached_port detector has been merged into the generic_database_assignment detector. The Google API Key detector now catches keys containing only one digit.
Ten new secret detectors addednew61how completely this was documenteddepth25/40specificity28/30actionability8/3061 / 100
Adds detectors for Brightcove OAuth credentials, Infor ION API Gateway OAuth client credentials (capturing the authorization host and token endpoint when present), generic Sanctum tokens, Telnyx API keys, Bifrost virtual keys (matched alone or together with the Bifrost deployment URL), Bitbucket HTTP access tokensaccess tokensA credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions. with the BBDC- prefix, Jira Data Center personal access tokenspersonal access tokensA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it., MetaApi cloud tokens, Appwrite instance encryption keys, and APIclub API keys.
Eight new secret analyzers addednew56how completely this was documenteddepth20/40specificity28/30actionability8/3056 / 100
Adds secret analyzers for AWS Cognito OAuth 2.0OAuth 2.0An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms. credentials with host, Alibaba Cloud IAMIAMIdentity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access. keys, Databricks access tokens with hostname, PyPI API tokens, Contentful Content Management API keys, DigitalOcean personal access tokens v1, DigitalOcean tokens, and DigitalOcean OAuth application tokens v1.
Figma token analyzer scope updateddeprecated48how completely this was documenteddepth20/40specificity20/30actionability8/3048 / 100
The Figma personal access tokenpersonal access tokenA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it. analyzer now reports the folders:read scope, replacing the deprecated projects:read scope.
GitGuardian Detection Engine 2.172 adds 10 new detectors, 8 new secret analyzers, and expanded recall for Scaleway, Salesforce, Splunk, and more.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds a new detector for Brightcove OAuth credentials.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds a new detector for Infor ION API Gateway OAuth client credentials, capturing the authorization host and token endpoint when present.
Adds a new detector for generic Sanctum tokens.
Adds a new detector for Telnyx API keys with the KEY prefix.
Adds a new detector for Bifrost virtual keys, matched alone or together with the Bifrost deployment URL.
+24 moreshow less
Adds a new detector for Bitbucket HTTP access tokensaccess tokensA credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions. with the BBDC- prefix.
Adds a new detector for Jira Data Center personal access tokenspersonal access tokensA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it..
Adds a new detector for MetaApi cloud tokens.
Adds a new detector for Appwrite instance encryption keys.
Adds a new detector for APIclub API keys.
Adds a checker for Artifactory reference tokens with custom host support.
Adds a checker for Splunk authentication tokens with custom host support.
Adds a new secret analyzer for AWS Cognito OAuth 2.0OAuth 2.0An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms. credentials with host.
Adds a new secret analyzer for Alibaba Cloud IAMIAMIdentity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access. keys.
Adds a new secret analyzer for Databricks access tokens with hostname.
Adds a new secret analyzer for PyPI API tokens.
Adds a new secret analyzer for Contentful Content Management API keys.
Adds a new secret analyzer for DigitalOcean personal access tokens v1.
Adds a new secret analyzer for DigitalOcean tokens.
Adds a new secret analyzer for DigitalOcean OAuth application tokens v1.
Expands the Scaleway Token detector to catch SCW_SECRET_KEY and SCALEWAY_SECRET_KEY assignments, including documents where the word scaleway is absent.
Expands the Splunk Authentication Token detector to also match an optional Splunk host alongside the token.
Expands the Salesforce OAuth2OAuth2An open authorization framework (RFC 6749) that lets a service grant limited access to a user's resources on another service without exposing credentials, giving cyber tools a standard way to authenticate against third-party APIs. Keys detector to capture the Salesforce instance host and validate against that instance's OAuth token endpoint (production or sandbox), returning failed_to_check when no host is found.
Expands the Username Password detector to also match Spanish, Portuguese, French, and Turkish username/password assignment keywords.
Expands the generic_high_entropy_secret detector to report secrets located near a localhost mention.
Expands the generic_encryption_key detector to report keys located near a localhost mention.
Merges the generic_database_assignment_attached_port detector into the generic_database_assignment detector.
Expands the Google API Key detector to catch keys containing only one digit.
Expands the Figma personal access tokenpersonal access tokenA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it. analyzer to report the folders:read scope, replacing the deprecated projects:read scope.
Adds a new detector for Brightcove OAuth credentials.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds a new detector for Infor ION API Gateway OAuth client credentials, capturing the authorization host and token endpoint when present.
Adds a new detector for generic Sanctum tokens.
Adds a new detector for Telnyx API keys with the KEY prefix.
Adds a new detector for Bifrost virtual keys, matched alone or together with the Bifrost deployment URL.
+15 moreshow less
Adds a new detector for Bitbucket HTTP access tokensaccess tokensA credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions. with the BBDC- prefix.
Adds a new detector for Jira Data Center personal access tokenspersonal access tokensA personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it..
Adds a new detector for MetaApi cloud tokens.
Adds a new detector for Appwrite instance encryption keys.
Adds a new detector for APIclub API keys.
Adds a checker for Artifactory reference tokens with custom host support.
Adds a checker for Splunk authentication tokens with custom host support.
Adds a new secret analyzer for AWS Cognito OAuth 2.0OAuth 2.0An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms. credentials with host.
Adds a new secret analyzer for Alibaba Cloud IAMIAMIdentity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access. keys.
Adds a new secret analyzer for Databricks access tokens with hostname.
Adds a new secret analyzer for PyPI API tokens.
Adds a new secret analyzer for Contentful Content Management API keys.
Adds a new secret analyzer for DigitalOcean personal access tokens v1.
Adds a new secret analyzer for DigitalOcean tokens.
Adds a new secret analyzer for DigitalOcean OAuth application tokens v1.
Capstone 6.0.0-Alpha11 adds x86 vendor-specific disassembly modes, gates Xtensa ESP32-S3/HIFI3 instructions behind a new mode flag, and adds PowerPC mcrxr instruction support.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
3 FEATURES0 OF 3 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
x86 vendor mode flags for AMD/Intelnew85how completely this was documenteddepth30/40specificity25/30actionability30/3085 / 100
Adds CS_MODE_X86_AMD and CS_MODE_X86_INTEL mode flags for x86 to enable vendor-specific disassembly behavior, currently affecting JO/JNO operand size and notation in 64-bit mode; default x86 behavior is unchanged.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Disassemble 64-bit x86 code using Intel vendor semantics so that JO/JNO operands are decoded according to Intel conventions.
python
csh = Cs(CS_ARCH_X86, CS_MODE_64 | CS_MODE_X86_INTEL)
for insn in csh.disasm(code, 0x1000):
    print('0x%x:\t%s\t%s' % (insn.address, insn.mnemonic, insn.op_str))
Disassemble 64-bit x86 code using AMD-style JO/JNO operand notation instead of the default representation.
python
cs = Cs(CS_ARCH_X86, CS_MODE_64 | CS_MODE_X86_AMD)
for i in cs.disasm(code, 0x1000):
    print(i.mnemonic, i.op_str)
Capstone 6.0.0-Alpha11 adds CS_MODE_X86_AMD/INTEL x86 vendor modes, CS_MODE_XTENSA_ESP32S3 gating, and PowerPC mcrxr instruction support.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ GET THIS VERSION
$ git clone --branch 6.0.0-Alpha11 https://github.com/capstone-engine/capstone.git
# already have the repo? check out this version:$ git checkout 6.0.0-Alpha11
└──▷ USE IT
Disassemble 64-bit x86 code using Intel vendor semantics so that JO/JNO operands are decoded according to Intel conventions.
python
csh = Cs(CS_ARCH_X86, CS_MODE_64 | CS_MODE_X86_INTEL)
for insn in csh.disasm(code, 0x1000):
print('0x%x:\t%s\t%s' % (insn.address, insn.mnemonic, insn.op_str))
Disassemble Xtensa firmware built for the ESP32-S3 to correctly decode ESP32-S3- and HIFI3-specific instructions that are otherwise gated off.
python
csh = Cs(CS_ARCH_XTENSA, CS_MODE_XTENSA_ESP32S3)
for insn in csh.disasm(firmware_bytes, 0x40000000):
    print('0x%x:\t%s\t%s' % (insn.address, insn.mnemonic, insn.op_str))
Adds CS_MODE_X86_AMD and CS_MODE_X86_INTEL mode flags for x86 to enable vendor-specific disassembly behavior (currently affecting JO/JNO operand size in 64-bit mode).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Gates Xtensa ESP32-S3 and HIFI3 instructions behind the new CS_MODE_XTENSA_ESP32S3 mode flag to avoid unintended decode on other Xtensa targets.
Capstone: Adds CS_MODE_X86_AMD and CS_MODE_X86_INTEL mode flags to select alternative x86 disassembly for JO/JNO operands in 64-bit mode; default x86 behavior is unchanged.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ USE IT
Disassemble 64-bit x86 code using AMD-style JO/JNO operand notation instead of the default representation.
python
cs = Cs(CS_ARCH_X86, CS_MODE_64 | CS_MODE_X86_AMD)
for i in cs.disasm(code, 0x1000):
print(i.mnemonic, i.op_str)
Disassemble Xtensa firmware built for the ESP32-S3 to expose ESP32-S3 and HIFI3 instructions that are hidden in the default mode.
python
cs = Cs(CS_ARCH_XTENSA, CS_MODE_XTENSA_ESP32S3)
for i in cs.disasm(firmware_bytes, 0x40000000):
    print(i.mnemonic, i.op_str)
Adds support for the mcrxr instruction in the PowerPC disassembly module.
EMBA v2.0.4 migrates firmware extraction to the actively maintained binwalk-ng fork, makes the local connector endpoint configurable, and completes CSV logging across all modules.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
3 FEATURES0 OF 3 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Configurable local connector endpoint and TCP settingsimproved65how completely this was documenteddepth20/40specificity25/30actionability20/3065 / 100
The local connector endpoint is now configurable, a change introduced via PR #2069, and MIN_TCP_SERV has been moved to defaults where it can be adjusted via scanning profiles.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
EMBA v2.0.4 migrates to binwalk-ng, makes the local connector endpoint configurable, and expands CSV logging across all modules.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ GET THIS VERSION
$ git clone --branch v2.0.4-summer_edition https://github.com/e-m-b-a/emba.git
# already have the repo? check out this version:$ git checkout v2.0.4-summer_edition
Makes the local connector endpoint configurable via the change introduced in PR #2069.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Moves MIN_TCP_SERV to defaults and allows it to be adjusted via scanning profiles.
Migrates firmware extraction from binwalk to the actively maintained binwalk-ng fork.
Completes CSV output logging across all modules for structured, machine-readable results.
Makes the local connector endpoint configurable via the change introduced in PR #2069.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Try professional password recovery, data decryption, mobile and cloud forensic tools from a manufacturer with 30+ years of expertise, providing tools and training to law enforcement, financial and intelligence agencies.
ElcomSoft's iOS Forensic Toolkit 10.11 extends bootloader-level full file system and keychain extraction beyond the A11 generation of Apple silicon, adding support for Apple Watch Series 4/5 and Apple TV 4K 2nd Gen, alongside updated OS compatibility.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
3 FEATURES0 OF 3 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Bootloader-level extraction for Apple TV 4K 2nd Gennew78how completely this was documenteddepth35/40specificity28/30actionability15/3078 / 100
Adds bootloader-level full file system and decrypted keychain extraction for Apple TV 4K 2nd Gen (A12 Bionic) via the usbliter8 SecureROM exploit, recovering accounts, authentication tokens, paired device records, network history, and Siri-related artifacts.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ This is the first time iOS Forensic Toolkit's low-level extraction has been extended past the A11 generation of Apple silicon.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
iOS Forensic Toolkit 10.11 brings bootloader-level full file system and keychain extraction to Apple Watch Series 4/5 and Apple TV 4K 2nd Gen.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds bootloader-level extraction for Apple Watch Series 4 and Series 5, producing a full file system image and decrypted keychain.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds bootloader-level extraction for Apple TV 4K 2nd Gen, producing a full file system image and decrypted keychain.
Extends low-level extraction support past the A11 generation of Apple silicon for the first time.
Adds bootloader-level extraction for Apple Watch Series 4 and Series 5, producing a full file system image and decrypted keychain.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds bootloader-level extraction for Apple TV 4K 2nd Gen, producing a full file system image and decrypted keychain.
ElcomSoft: Adds bootloader-level keychain and full file system extraction for Apple TV 4K 2nd Gen (A12 Bionic) via the usbliter8 SecureROM exploit, recovering accounts, authentication tokens, paired device records, network history, and Siri-related artifacts.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Network forensics, packet sniffers and IT security products. Download NetworkMiner and other free software for network security analysis.
Netresec's FlowCarp gained statistical C2 protocol classification with custom model training, plus a free public demo API classifying traffic against 600+ known protocols.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
1 FEATURE0 OF 1 FEATUREmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Free demo API for C2 protocol identificationnew75how completely this was documenteddepth20/40specificity25/30actionability30/3075 / 100
A free demo server at demo.flowcarp.com supports identifying 600+ known C2 protocols without a local FlowCarp install; a PCAPPCAPA packet capture, recorded network packets that can be inspected later. Analysts use it to reconstruct communication and investigate protocol behavior or suspicious traffic. can be submitted directly via curl --data-binary @dump.pcap https://demo.flowcarp.com.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Submit a PCAP to the free demo server during triage to instantly identify C2 protocols across 600+ known families without a local FlowCarp install.
FlowCarp adds statistical C2 protocol classification and a free demo API at demo.flowcarp.com supporting 600+ protocols︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Train a custom protocol model from sandbox C2 captures so FlowCarp can recognize a previously unknown malware family in future PCAPsPCAPsA packet capture, recorded network packets that can be inspected later. Analysts use it to reconstruct communication and investigate protocol behavior or suspicious traffic..
Classify traffic in a new PCAPPCAPA packet capture, recorded network packets that can be inspected later. Analysts use it to reconstruct communication and investigate protocol behavior or suspicious traffic. against your custom model to confirm C2 protocol matches across different samples or sandbox runs.
tcpdump 4.99.7 deepens MPTCPMPTCPA TCP extension (RFC 8684) that lets a single connection use multiple network paths simultaneously, increasing throughput and resilience; tools use it to keep sessions alive across interface changes. option dissection, adds TCP AccECNAccECNA TCP extension that carries more precise congestion-signal counts between endpoints than classic ECN, letting senders tune their rate with finer feedback from ECN-capable networks. flag decoding, and warns when --count is misused on the command line.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
3 FEATURES0 OF 3 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Expanded MPTCP option dissectionimproved64how completely this was documenteddepth28/40specificity26/30actionability10/3064 / 100
Adds dissection of the MPTCP MP_TCPRST sub-option (subtype 0x8), including the U/V/W/T flags and reset reasons such as Middlebox interference.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Also parses the data_len field in the MPTCP MP_CAPABLE option and prints all eight capability flags (A through H).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
— Names sub-option, subtype code, and all flags; no usage example giventcpdump-4.99.7
thinner coverage below
0200
Warning for misused --count flagimproved51how completely this was documenteddepth16/40specificity20/30actionability15/3051 / 100
Adds an error message when --count is used without -r or -V, flagging a common command-line mistake.
— Names exact flags involved; clear condition to testtcpdump-4.99.7
0300
TCP AccECN flag decodingnew34how completely this was documenteddepth14/40specificity14/30actionability6/3034 / 100
Adds support for decoding the TCP AE (AccECN) flag in TCP header output.
— Names the flag but gives no mechanism or example outputtcpdump-4.99.7
tcpdump 4.99.7 extends MPTCPMPTCPA TCP extension (RFC 8684) that lets a single connection use multiple network paths simultaneously, increasing throughput and resilience; tools use it to keep sessions alive across interface changes. dissection, adds TCP AccECNAccECNA TCP extension that carries more precise congestion-signal counts between endpoints than classic ECN, letting senders tune their rate with finer feedback from ECN-capable networks. flag support, and warns on misused --count.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ GET THIS VERSION
$ git clone --branch tcpdump-4.99.7 https://github.com/the-tcpdump-group/tcpdump.git
# already have the repo? check out this version:$ git checkout tcpdump-4.99.7
Adds an error message when --count is used without -r or -V.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds dissection of the MPTCP MP_TCPRST sub-option (subtype 0x8), including U/V/W/T flags and reset reasons such as Middlebox interference.
Parses the data_len field in the MPTCP MP_CAPABLE option and prints all eight capability flags (A through H).
Adds support for decoding the TCP AE (AccECN) flag in TCP header output.
Adds an error message when --count is used without -r or -V.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds dissection of the MPTCP MP_TCPRST sub-option (subtype 0x8), including U/V/W/T flags and reset reasons such as Middlebox interference.
Adds support for decoding the TCP AE (AccECN) flag in TCP header output.
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
SO-CRATES v4.2.0 focuses on hardening deployment and API security, adding a reverse-proxy hostname allowlist, enforcing JSON content-type on API calls, and restricting default port exposure.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
3 FEATURES0 OF 3 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
ALLOWED_HOSTS environment variable for reverse proxiesbreaking78how completely this was documenteddepth25/40specificity25/30actionability28/3078 / 100
Adds the ALLOWED_HOSTS environment variable (e.g.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ -e ALLOWED_HOSTS='*.killercoda.com') to support serving SO-CRATES behind a reverse proxy or cloud hostname.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Browsing via IP or localhost requires no change, but deployments behind a proxy or cloud hostname must now set this variable or they will error out.
Run SO-CRATES behind a Killercoda (or other cloud/reverse-proxy) hostname so the host validation passes.
$ docker run -e ALLOWED_HOSTS='*.killercoda.com' so-crates
— Names exact env var and example command, but no deeper mechanism givenv4.2.0
0200
Localhost-only port binding in compose filesbreaking65how completely this was documenteddepth20/40specificity20/30actionability25/3065 / 100
Docker/Podman compose files now publish the port on localhost only by default; to allow other hosts on the network to reach SO-CRATES, change the port mapping to "8000:8000".
— Exact config change given, but limited explanation of underlying mechanismv4.2.0
thinner coverage below
0300
JSON API content-type enforcementbreaking45how completely this was documenteddepth15/40specificity15/30actionability15/3045 / 100
Scripts calling the JSON API must now send Content-Type: application/json; requests omitting this header will fail where they previously succeeded.
— Clear requirement stated but no example request or endpoint givenv4.2.0
└──▷ BREAKING ON UPGRADE
!
Serving SO-CRATES behind a reverse proxy or cloud hostname now requires setting the ALLOWED_HOSTS environment variable (e.g. -e ALLOWED_HOSTS='*.killercoda.com'); omitting it will produce an error.
!
Docker/Podman compose files now bind the port to localhost only; setups relying on other machines reaching SO-CRATES on the network must change the port mapping to "8000:8000".
!
Scripts calling the JSON API must now send Content-Type: application/json; requests without this header will break.
SO-CRATES v4.2.0 adds ALLOWED_HOSTS env var for reverse-proxy deployments and tightens JSON API content-type enforcement.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ GET THIS VERSION
$ git clone --branch v4.2.0 https://github.com/dougburks/so-crates.git
# already have the repo? check out this version:$ git checkout v4.2.0
└──▷ TRY IT
Run SO-CRATES behind a Killercoda (or other cloud/reverse-proxy) hostname so the host validation passes.
$ docker run -e ALLOWED_HOSTS='*.killercoda.com' so-crates
Adds ALLOWED_HOSTS environment variable (e.g.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ -e ALLOWED_HOSTS='*.killercoda.com') to support serving SO-CRATES behind a reverse proxy or cloud hostname; browsing via IP or localhost requires no change.
Requires scripts calling the JSON API to send Content-Type: application/json; requests omitting this header will now fail.
Docker/Podman compose files now publish the port on localhost only by default; change the port mapping to "8000:8000" to allow other hosts on the network.
Adds ALLOWED_HOSTS environment variable (e.g.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ -e ALLOWED_HOSTS='*.killercoda.com') to support serving SO-CRATES behind a reverse proxy or cloud hostname; browsing via IP or localhost requires no change.
2 more in Everything
└──▷ BREAKING ON UPGRADE
!Serving SO-CRATES behind a reverse proxy or cloud hostname now requires setting the ALLOWED_HOSTS environment variable (e.g. -e ALLOWED_HOSTS='*.killercoda.com'); omitting it will produce an error.
!Docker/Podman compose files now bind the port to localhost only; setups relying on other machines reaching SO-CRATES on the network must change the port mapping to "8000:8000".
!Scripts calling the JSON API must now send Content-Type: application/json; requests without this header will break.
Sophos Switch is a network orchestration platform enabling centralized management and security policy enforcement across switching infrastructure.
Sophos Switch now surfaces switch names as the primary identifier across management pages and lets admins search by name.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
1 FEATURE0 OF 1 FEATUREmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Switch names as primary identifier with searchimproved50how completely this was documenteddepth20/40specificity15/30actionability15/3050 / 100
Switch, site, and stack management pages in Sophos Central now display switch names as the primary identifier instead of other identifiers, and the search box on these pages supports searching for switches by name.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Welcome to the comprehensive documentation for Aviatrix's cloud networking platform. Here you'll find everything you need to deploy, configure, and manage your multi-cloud networking infrastructure.
Aviatrix launched Harvest and Decrypt Protection, a single software policy combining post-quantumpost-quantumCryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA.ML-KEMML-KEMNIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake. encryption, Communication Governance, and a two-level Containment Assessment tool, alongside a new crypto visibility inventory and a free tier for early adopters.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
5 FEATURES1 OF 5 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0101
Post-quantum ML-KEM encryption with crypto agilitynew70how completely this was documenteddepth30/40specificity25/30actionability15/3070 / 100
Aviatrix adds post-quantum key exchangepost-quantum key exchangeA cryptographic handshake algorithm designed to resist attacks from quantum computers, using math problems like lattices that quantum algorithms cannot efficiently solve, letting tools stay secure against future quantum-capable adversaries. using the ML-KEM standard on the control plane across Aviatrix-encrypted paths, making intercepted traffic unreadable to future quantum computers without a hardware refresh or network redesign.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ The post-quantum algorithm is exposed as a configuration setting — crypto agility — so it can be swapped via a configuration push rather than a hardware refresh cycle.
— Names the ML-KEM standard and swap mechanism, but no exact config commandlaunch-20260922-5ef39c4a
0200
Containment Assessment tool with level 2 runtime analysisnew70how completely this was documenteddepth30/40specificity25/30actionability15/3070 / 100
A self-service Containment Assessment tool tests five properties of the cloud estate and returns a provisional Blast Radius and harvest exposure read in approximately five minutes. Containment Assessment level 2 extends this with a read-only, agentless engagement against live runtime flows that quantifies exposure as Reachable Value at Risk in dollars, before any policy is written.
Communication Governance workload policy enforcementnew55how completely this was documenteddepth25/40specificity20/30actionability10/3055 / 100
Communication Governance runs on the same gateways that handle encryption, enforcing explicit workload-to-workload reachability policy at the granularity of workload identityworkload identityAn identity assigned to software, such as a service or container, rather than a person. It lets the workload authenticate and receive permissions without sharing a user's credentials. and protocol on every available path.
Free tier and trial for Harvest and Decrypt Protectionnew45how completely this was documenteddepth15/40specificity20/30actionability10/3045 / 100
Harvest and Decrypt Protection is available at no cost for the first five policies and five nodes for existing customers, with no license and no time limit; new customers receive a 30-day free trial.
Cryptographic traffic inventory (crypto visibility)new43how completely this was documenteddepth20/40specificity15/30actionability8/3043 / 100
Extends the quantum-safequantum-safeCryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA. roadmap with crypto visibility: a network-path cryptographic inventory mapping which applications communicate in cleartext, what they depend on, and where they communicate.
Aviatrix launches Harvest and Decrypt Protection: post-quantumpost-quantumCryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA.ML-KEMML-KEMNIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake. encryption plus Communication Governance in one software policy, free for first five policies.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds post-quantum key exchangepost-quantum key exchangeA cryptographic handshake algorithm designed to resist attacks from quantum computers, using math problems like lattices that quantum algorithms cannot efficiently solve, letting tools stay secure against future quantum-capable adversaries. using the ML-KEM standard on the control plane across Aviatrix-encrypted paths, making intercepted traffic unreadable to future quantum computers without a hardware refresh or network redesign.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Introduces Communication Governance on the same gateways that handle encryption, enforcing explicit workload-to-workload reachability policy at the granularity of workload identityworkload identityAn identity assigned to software, such as a service or container, rather than a person. It lets the workload authenticate and receive permissions without sharing a user's credentials. and protocol on every available path.
Provides crypto agility as a configuration setting — the post-quantum algorithm can be swapped with a configuration push rather than a hardware refresh cycle.
Adds a self-service Containment Assessment tool that tests five properties of the cloud estate and returns a provisional Blast Radius and harvest exposure read in approximately five minutes.
Adds a Containment Assessment level 2 — a read-only, agentless engagement against live runtime flows that quantifies exposure as Reachable Value at Risk in dollars, before any policy is written.
+2 moreshow less
Extends the quantum-safequantum-safeCryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA. roadmap with crypto visibility: a network-path cryptographic inventory mapping which applications communicate in cleartext, what they depend on, and where they communicate.
Harvest and Decrypt Protection is available at no cost for the first five policies and five nodes for existing customers, with no license and no time limit; new customers receive a 30-day free trial.
Palo Alto Networks provides cybersecurity platforms for threat prevention, detection, and response across networks, cloud, and endpoints.
Palo Alto Networks launched Unit 42 Continuous Frontier AI Defense, an always-on agentic offensive security service that combines a continuous testing engine, a multi-model AI harness, and adversary simulation to find, validate, and remediate enterprise exposures.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
4 FEATURES4 OF 4 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0101
Continuous Testing Enginenew65how completely this was documenteddepth30/40specificity25/30actionability10/3065 / 100
Performs a full-estate baseline scan followed by always-on testing as an organization's environment changes, covering web apps, APIs, cloud infrastructure, source code repositories, and network assets.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Multi-Model AI Harness for offensive security tasksnew60how completely this was documenteddepth30/40specificity25/30actionability5/3060 / 100
Routes offensive security tasks to the model best suited for each job, addressing the finding that no single model catches more than 40% of vulnerabilities and that leading models share less than 10% overlap in identified exposures.
Unit 42 Continuous Frontier AI Defense servicenew58how completely this was documenteddepth25/40specificity25/30actionability8/3058 / 100
A new always-on agentic offensive security service that continuously finds, validates, and remediates enterprise exposures using proprietary multi-model AI harnesses powered by Anthropic Claude Mythos 5 and OpenAI GPT-5.6-Cyber.
Advanced Adversary Simulationnew50how completely this was documenteddepth25/40specificity20/30actionability5/3050 / 100
Proves real-world exploitability by validating end-to-end attack pathsattack pathsA possible sequence of steps an attacker could take to reach a valuable target. It connects weaknesses, permissions and reachable systems rather than treating each finding separately. across first- and third-party web apps, APIs, cloud infrastructure, source code repositories, and network assets.
— Describes purpose and scope but no concrete usage detail2026-09-22-d8eee514
Palo Alto Networks launches Unit 42 Continuous Frontier AI Defense, an always-on agentic offensive security service powered by Anthropic Claude Mythos 5 and OpenAI GPT-5.6-Cyber.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Introduces Unit 42 Continuous Frontier AI Defense, a new always-on agentic offensive security service that continuously finds, validates, and remediates enterprise exposures using proprietary multi-model AI harnesses with Anthropic Claude Mythos 5 and OpenAI GPT-5.6-Cyber.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds a Continuous Testing Engine that performs a full-estate baseline scan followed by always-on testing as an organization's environment changes, covering web apps, APIs, cloud infrastructure, source code repositories, and network assets.
Introduces a proprietary Multi-Model AI Harness that routes offensive security tasks to the model best suited for each job, addressing the finding that no single model catches more than 40% of vulnerabilities and that leading models share less than 10% overlap in identified exposures.
Delivers Advanced Adversary Simulation that proves real-world exploitability by validating end-to-end attack pathsattack pathsA possible sequence of steps an attacker could take to reach a valuable target. It connects weaknesses, permissions and reachable systems rather than treating each finding separately. across first- and third-party web apps, APIs, cloud infrastructure, source code repositories, and network assets.
Falco 0.45.0 introduces raw byte matching in rule conditions and output, reload control endpoints, and GPUGPUA graphics processing unit, a processor that performs many calculations in parallel. AI workloads use GPUs to speed up model training and inference. resource hijacking detection rules, alongside a set of breaking changes covering driver API compatibility, modern eBPFeBPFA Linux technology for running verified programs inside the kernel without changing its source. Tools use it to observe processes, enforce rules and process network traffic. memory usage, container configuration keys, and package upgrade behavior.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
9 FEATURES4 OF 9 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Reload control endpointsnew90how completely this was documenteddepth30/40specificity30/30actionability30/3090 / 100
Adds a GET /reload webserver endpoint reporting process identity, reload generation, and readiness so integrations can verify a completed reload, plus a new reload_control configuration key that opens a Unix socket accepting POST /reload for local reload requests (disabled by default).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Container plugin engine_timeout optionnew90how completely this was documenteddepth30/40specificity30/30actionability30/3090 / 100
Adds an engine_timeout option to the container plugin (defaults to 10 seconds) to prevent an unresponsive runtime socket from blocking Falco startup indefinitely; set to 0 to disable.
Raw byte matching in rule conditions and outputbreaking85how completely this was documenteddepth35/40specificity25/30actionability25/3085 / 100
Adds \xHH byte escape syntax in rule conditions for matching filenames or process arguments containing arbitrary bytes not representable as valid UTF-8, and now preserves raw bytes when extracting field values for rule matching rather than sanitized replacements. Both text and JSON alert output now escape control characters and replace invalid UTF-8 sequences for printable output; rule conditions and output consumers that relied on the old UTF-8 sanitization behavior will behave differently and should be reviewed after upgrading.
Write a rule that detects a process argument containing a specific non-UTF-8 byte sequence, now possible with raw byte escapes.
yaml
- rule: Suspicious Raw Byte Argument
  desc: Detects a process argument containing a specific non-UTF-8 byte
  condition: proc.args contains \xc0\xae
  output: 'Suspicious raw byte in argument (proc=%proc.name args=%proc.args)'
  priority: WARNING
GPU resource hijacking detection rulesnew80how completely this was documenteddepth25/40specificity30/30actionability25/3080 / 100
Adds two sandbox rules — Container Accessing GPU Device and GPU Management Tool Run in Container — for detecting GPU resource hijacking inside containers; both are disabled by default and require tuning the user_known_gpu_workloads list before enabling.
Driver selection controls for package upgradesbreaking80how completely this was documenteddepth30/40specificity25/30actionability25/3080 / 100
Supports FALCO_DRIVER_CHOICE=none to skip driver setup and FALCOCTL_DRIVER_VERSION to specify an explicit driver version during DEB/RPM package upgrade transactions. DEB/RPM upgrades now also start the selected Falco service and install the driver automatically, so unattended upgrade scripts and custom driver pins must be reviewed to avoid unintended changes.
Modern eBPF driver buffer and drop-tracking improvementsbreaking75how completely this was documenteddepth35/40specificity25/30actionability15/3075 / 100
The modern eBPF probe now uses two auxiliary buffers per CPUCPUThe main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware. to protect event construction on preemptible kernels, with graceful fallback and a warning on kernels lacking required BPFBPFA Linux kernel virtual machine that lets programs attach small, sandboxed bytecode filters to kernel hooks — syscalls, network events, tracepoints — so cyber tools can observe or redirect kernel behaviour without writing a kernel module. atomic operations — this doubles auxiliary map memory usage per CPU, so capacity should be reviewed before upgrading. New eBPF counters expose drops caused by reentrancy and exhausted auxiliary buffers, and CPU migrations, to help distinguish preemption-related capture pressure from other drop causes.
container_engines.* configuration removedbreaking70how completely this was documenteddepth20/40specificity25/30actionability25/3070 / 100
The container_engines.* configuration keys have been removed from the configuration schema; migrate to the container plugin configuration (e.g. engines.cri.sockets) instead.
Container plugin background metadata retrievalimproved50how completely this was documenteddepth25/40specificity15/30actionability10/3050 / 100
Container plugin 0.7.4 keeps already-collected container metadata and retrieves missing container info in the background when an initial listing is interrupted at startup.
Falco 0.45.0 refuses to load kernel modules or probes not compatible with driver API 11.0.0 — deploy updated drivers before upgrading.
!
Modern eBPF now uses two auxiliary buffers per CPU, doubling auxiliary map memory per CPU — account for this before upgrading.
!
Rule conditions that relied on UTF-8 sanitization before comparisons will behave differently; review and update custom rules accordingly.
!
Output consumers that parsed Falco's formatted text or JSON output must account for the new control-character escaping and invalid-UTF-8 replacement.
!
The container_engines.* configuration keys have been removed from the configuration schema — migrate to the container plugin configuration (e.g. engines.cri.sockets) instead.
!
DEB/RPM upgrades now start the selected Falco service and install the driver — unattended upgrade scripts and custom driver pins must be reviewed to avoid unintended changes.
Falco 0.45.0 adds raw byte matching in rules, reload control endpoints, and GPUGPUA graphics processing unit, a processor that performs many calculations in parallel. AI workloads use GPUs to speed up model training and inference. detection rules︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ USE IT
Write a rule that detects a process argument containing a specific non-UTF-8 byte sequence, now possible with raw byte escapes.
/etc/falco/rules.d/raw_byte.yaml
- rule: Suspicious Raw Byte Argument
  desc: Detects a process argument containing a specific non-UTF-8 byte
  condition: proc.args contains \xc0\xae
  output: 'Suspicious raw byte in argument (proc=%proc.name args=%proc.args)'
  priority: WARNING
Adds GET /reload webserver endpoint reporting process identity, reload generations, and readiness so integrations can verify a completed reload.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds reload_control configuration key that opens a Unix socket accepting POST /reload for local reload requests (disabled by default).
Adds \xHH byte escape syntax in rule conditions for matching filenames or process arguments containing arbitrary bytes not representable as valid UTF-8.
Adds engine_timeout option to the container plugin (defaults to 10 seconds) to prevent an unresponsive runtime socket from blocking Falco startup indefinitely; set to 0 to disable.
Adds two sandbox rules — Container Accessing GPU Device and GPU Management Tool Run in Container — for detecting GPU resource hijacking inside containers (both disabled by default; tune user_known_gpu_workloads before enabling).
+6 moreshow less
Adds new eBPFeBPFA Linux technology for running verified programs inside the kernel without changing its source. Tools use it to observe processes, enforce rules and process network traffic. counters exposing drops caused by reentrancy and exhausted auxiliary buffers, and CPUCPUThe main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware. migrations, to help distinguish preemption-related capture pressure from other drop causes.
Supports FALCO_DRIVER_CHOICE=none to skip driver setup and FALCOCTL_DRIVER_VERSION to specify an explicit driver version during DEB/RPM package upgrade transactions.
Preserves raw bytes when extracting field values for rule matching, so rule conditions now see original bytes rather than sanitized replacements.
Both text and JSON output now escape control characters and replace invalid UTF-8 sequences for printable alert output.
Modern eBPF probe uses two auxiliary buffers per CPU to protect event construction on preemptible kernels, with graceful fallback and a warning on kernels lacking required BPFBPFA Linux kernel virtual machine that lets programs attach small, sandboxed bytecode filters to kernel hooks — syscalls, network events, tracepoints — so cyber tools can observe or redirect kernel behaviour without writing a kernel module. atomic operations.
Container plugin 0.7.4 keeps already-collected metadata and retrieves missing container info in the background when an initial listing is interrupted at startup.
Adds GET /reload webserver endpoint reporting process identity, reload generations, and readiness so integrations can verify a completed reload.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds reload_control configuration key that opens a Unix socket accepting POST /reload for local reload requests (disabled by default).
Adds \xHH byte escape syntax in rule conditions for matching filenames or process arguments containing arbitrary bytes not representable as valid UTF-8.
Adds two sandbox rules — Container Accessing GPU Device and GPU Management Tool Run in Container — for detecting GPU resource hijacking inside containers (both disabled by default; tune user_known_gpu_workloads before enabling).
Adds new eBPFeBPFA Linux technology for running verified programs inside the kernel without changing its source. Tools use it to observe processes, enforce rules and process network traffic. counters exposing drops caused by reentrancy and exhausted auxiliary buffers, and CPUCPUThe main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware. migrations, to help distinguish preemption-related capture pressure from other drop causes.
6 more in Everything
└──▷ BREAKING ON UPGRADE
!Falco 0.45.0 refuses to load kernel modules or probes not compatible with driver API 11.0.0 — deploy updated drivers before upgrading.
!Modern eBPF now uses two auxiliary buffers per CPU, doubling auxiliary map memory per CPU — account for this before upgrading.
!Rule conditions that relied on UTF-8 sanitization before comparisons will behave differently; review and update custom rules accordingly.
!Output consumers that parsed Falco's formatted text or JSON output must account for the new control-character escaping and invalid-UTF-8 replacement.
!The container_engines.* configuration keys have been removed from the configuration schema — migrate to the container plugin configuration (e.g. engines.cri.sockets) instead.
!DEB/RPM upgrades now start the selected Falco service and install the driver — unattended upgrade scripts and custom driver pins must be reviewed to avoid unintended changes.
Low-level unprivileged sandboxing tool used by Flatpak and similar projects
Bubblewrap v0.13.0 adds mount flag remounting via mount_setattr()mount_setattr()A Linux system call, added in kernel 5.12, that changes attributes on a mount point or an entire mount tree atomically, letting cyber tools adjust propagation flags and ID mappings without remounting., tightens path argument validation, and introduces an opt-in debug logging build option.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
3 FEATURES0 OF 3 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Debug logging build optionnew80how completely this was documenteddepth25/40specificity25/30actionability30/3080 / 100
A new -Ddebug_logging=true Meson build option enables verbose debug logging in bubblewrap, gated at runtime by the DEBUG_INVOCATION environment variable so builds can ship with the capability without enabling it by default.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Build bubblewrap with debug logging enabled, then trigger verbose output for a sandboxed invocation to trace mount_setattr calls.
— Names exact build flag and env var with runnable examplev0.13.0
thinner coverage below
0200
Empty path arguments now rejectedbreaking55how completely this was documenteddepth20/40specificity20/30actionability15/3055 / 100
Path arguments such as --bind and --overlay-src now reject empty strings instead of silently treating them as the root directory, changing prior behavior where an empty path implicitly meant /.
— Names affected flags and before/after behavior, no examplev0.13.0
0300
mount_setattr() for mount flag remountingnew25how completely this was documenteddepth10/40specificity10/30actionability5/3025 / 100
Bubblewrap v0.13.0 adds use of mount_setattr() for remounting mount flags, per the release summary; no further mechanism or affected options are described.
— Only mentioned in summary, no detail or example givenv0.13.0
Bubblewrap v0.13.0 adds mount_setattr()mount_setattr()A Linux system call, added in kernel 5.12, that changes attributes on a mount point or an entire mount tree atomically, letting cyber tools adjust propagation flags and ID mappings without remounting. for mount flag remounting, rejects empty path args, and introduces -Ddebug_logging=true with DEBUG_INVOCATION︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ GET THIS VERSION
$ git clone --branch v0.13.0 https://github.com/containers/bubblewrap.git
# already have the repo? check out this version:$ git checkout v0.13.0
└──▷ TRY IT
Build bubblewrap with debug logging enabled, then trigger verbose output for a sandboxed invocation to trace mount_setattr calls.
Adds -Ddebug_logging=true build option to enable verbose debug logging, gated at runtime by the DEBUG_INVOCATION environment variable.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Path arguments such as --bind and --overlay-src now reject empty strings instead of silently treating them as the root directory.
Adds -Ddebug_logging=true build option to enable verbose debug logging, gated at runtime by the DEBUG_INVOCATION environment variable.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Rapid7 InsightCloudSec's September release extends CrowdStrike Falcon Query Filters to Oracle Cloud Infrastructure and adds a wave of Azure detection capability spanning Cosmos DB authentication/encryption/network posture and MySQL/PostgreSQL Flexible Server private endpoint and public-access checks.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Rapid7 InsightCloudSec provides cloud security posture management and compliance monitoring across multi-cloud environments.
Rapid7 InsightCloudSec's September release extends CrowdStrike Falcon Query Filters to Oracle Cloud Infrastructure and adds a wave of Azure detection capability spanning Cosmos DB authentication/encryption/network posture and MySQL/PostgreSQL Flexible Server private endpoint and public-access checks.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
4 FEATURES1 OF 4 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0101
Cosmos DB authentication, encryption and network posture detectionnew90how completely this was documenteddepth35/40specificity30/30actionability25/3090 / 100
Adds harvesting of the disableLocalAuth property and firewall IP rules (including 0.0.0.0 datacenter-access detection) for Azure Distributed Table (Cosmos DB) resources, plus three new Query Filters — Distributed Table Local Authentication Configuration (default: enabled), Distributed Table Encryption Configuration (default: provider-managed), and Distributed Table Without Network Traffic Restrictions — and three matching Insights: Distributed Table With Local Authentication Enabled, Distributed Table Encrypted With Provider Managed Key, and Distributed Table Without Network Traffic Restrictions.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
— Names every harvested field, filter and insight with defaults2026-09-22-687ac038
0200
Azure MySQL/PostgreSQL Flexible Server private endpoint and auth checksnew90how completely this was documenteddepth35/40specificity30/30actionability25/3090 / 100
Adds harvesting of private endpoint connection counts for Azure Database for MySQL and PostgreSQL Flexible Servers, plus three new Query Filters — Database Instance Microsoft Entra-Only Authentication (default: not configured), Database Instance Flexible Private Endpoint Connections (configurable by engine type, default: MySQL Flexible Servers without private endpoints), and Database Instance Firewall Allows Public Ingress (flags a rule with start IP 0.0.0.0 and end IP other than 0.0.0.0, excluding the Azure services-only 0.0.0.0–0.0.0.0 rule) — and five new Insights: Database Instance Without Microsoft Entra-Only Authentication (MySQL), Database Instance Without Private Endpoint (MySQL Flexible Server), PostgreSQL Database Instance With Public Network Access Enabled, PostgreSQL Database Instance Without Private Endpoint Connection, and Database Instance Firewall Allows Public Ingress (SQL Server).
— Enumerates every filter and insight with concrete criteria2026-09-22-687ac038
0300
PostgreSQL log retention insight parameter matchingimproved75how completely this was documenteddepth30/40specificity25/30actionability20/3075 / 100
Updates the Database Instance Log Retention Below Threshold (PostgreSQL) Insight to detect Azure PostgreSQL Flexible Servers where logfiles.retention_days is set to 3 days or fewer, and updates the Database Instance With Setting Below Threshold log_retention_days (PostgreSQL) Insight to match both the legacy log_retention_days and updated logfiles.retention_days parameter names using an OR condition.
CrowdStrike Falcon Query Filter for OCInew53how completely this was documenteddepth20/40specificity18/30actionability15/3053 / 100
Extends CrowdStrike Falcon agent Query Filters to Oracle Cloud Infrastructure (OCIOCIOpen Container Initiative standard, maintained by the Linux Foundation, defining the image format and runtime spec that container tools share so images built once run anywhere OCI-compliant.) compute instances, joining existing AWS, Azure, and GCP coverage, enabling security teams to identify OCI instances by Falcon agent presence.
— Names platform coverage but not the filter's exact label2026-09-22-687ac038
InsightCloudSec 26.9.22 adds CrowdStrike Falcon OCIOCIOpen Container Initiative standard, maintained by the Linux Foundation, defining the image format and runtime spec that container tools share so images built once run anywhere OCI-compliant. support, seven new Azure Insights, and six new Query Filters for Cosmos DB, MySQL, and PostgreSQL.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Extends CrowdStrike Falcon agent Query Filters to Oracle Cloud Infrastructure (OCI) compute instances, joining existing AWS, Azure, and GCP coverage — enabling security teams to identify OCI instances by Falcon agent presence.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds harvesting of the disableLocalAuth property and firewall IP rules (including 0.0.0.0 datacenter-access detection) for Azure Distributed Table (Cosmos DB) resources.
Adds harvesting of private endpoint connection counts for Azure Database for MySQL and PostgreSQL Flexible Servers.
Adds Distributed Table Local Authentication Configuration Query Filter to identify Cosmos DB accounts by whether local (key-based) authentication is enabled or disabled (default: enabled).
Adds Distributed Table Encryption Configuration Query Filter to identify Cosmos DB accounts by customer-managed vs. provider-managed encryption keys (default: provider-managed).
+14 moreshow less
Adds Distributed Table Without Network Traffic Restrictions Query Filter to identify Cosmos DB accounts that allow all network traffic or have 0.0.0.0 in firewall IP rules.
Adds Database Instance Microsoft Entra-Only Authentication Query Filter to identify Database Instances by Entra-only authentication status (default: not configured).
Adds Database Instance Flexible Private Endpoint Connections Query Filter to identify Azure Flexible Servers by private endpoint connection status, configurable by engine type (default: MySQL Flexible Servers without private endpoints).
Adds Database Instance Firewall Allows Public Ingress Query Filter to flag Database Instances with a firewall rule whose start IP is 0.0.0.0 and end IP is any address other than 0.0.0.0 (Azure services-only rule 0.0.0.0–0.0.0.0 is not flagged).
Adds Distributed Table With Local Authentication Enabled Insight to identify Azure Cosmos DB accounts using key-based authentication instead of Microsoft Entra IDEntra IDMicrosoft's cloud-based identity and access management service, formerly Azure Active Directory, used by cyber tools to authenticate users and enforce access policies in Microsoft 365 and Azure environments. only.
Adds Distributed Table Encrypted With Provider Managed Key Insight to identify Azure Cosmos DB accounts using service-managed rather than customer-managed keys.
Adds Distributed Table Without Network Traffic Restrictions Insight to identify Azure Cosmos DB accounts with unrestricted network access or 0.0.0.0 in firewall rules.
Adds Database Instance Without Microsoft Entra-Only Authentication (MySQL) Insight to identify Azure Database for MySQL Flexible Servers lacking Entra-only authentication.
Adds Database Instance Without Private Endpoint (MySQL Flexible Server) Insight to identify Azure Database for MySQL Flexible Servers without private endpoints.
Adds PostgreSQL Database Instance With Public Network Access Enabled Insight to identify PostgreSQL instances with public network access enabled.
Adds PostgreSQL Database Instance Without Private Endpoint Connection Insight to identify Azure Database for PostgreSQL Flexible Servers without a private endpoint connection.
Adds Database Instance Firewall Allows Public Ingress (SQL Server) Insight to flag SQL Server instances with a firewall rule permitting public ingress (start IP 0.0.0.0, end IP anything other than 0.0.0.0).
Updates Database Instance Log Retention Below Threshold (PostgreSQL) Insight to detect Azure PostgreSQL Flexible Servers where logfiles.retention_days is set to 3 days or fewer, supporting both the legacy log_retention_days and updated logfiles.retention_days parameter names.
Updates Database Instance With Setting Below Threshold log_retention_days (PostgreSQL) Insight to match both log_retention_days and logfiles.retention_days parameter names using an OR condition.
Extends CrowdStrike Falcon agent Query Filters to Oracle Cloud Infrastructure (OCI) compute instances, joining existing AWS, Azure, and GCP coverage — enabling security teams to identify OCI instances by Falcon agent presence.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds harvesting of the disableLocalAuth property and firewall IP rules (including 0.0.0.0 datacenter-access detection) for Azure Distributed Table (Cosmos DB) resources.
Adds harvesting of private endpoint connection counts for Azure Database for MySQL and PostgreSQL Flexible Servers.
Adds Distributed Table Local Authentication Configuration Query Filter to identify Cosmos DB accounts by whether local (key-based) authentication is enabled or disabled (default: enabled).
Adds Distributed Table Encryption Configuration Query Filter to identify Cosmos DB accounts by customer-managed vs. provider-managed encryption keys (default: provider-managed).
+12 moreshow less
Adds Distributed Table Without Network Traffic Restrictions Query Filter to identify Cosmos DB accounts that allow all network traffic or have 0.0.0.0 in firewall IP rules.
Adds Database Instance Microsoft Entra-Only Authentication Query Filter to identify Database Instances by Entra-only authentication status (default: not configured).
Adds Database Instance Flexible Private Endpoint Connections Query Filter to identify Azure Flexible Servers by private endpoint connection status, configurable by engine type (default: MySQL Flexible Servers without private endpoints).
Adds Database Instance Firewall Allows Public Ingress Query Filter to flag Database Instances with a firewall rule whose start IP is 0.0.0.0 and end IP is any address other than 0.0.0.0 (Azure services-only rule 0.0.0.0–0.0.0.0 is not flagged).
Adds Distributed Table With Local Authentication Enabled Insight to identify Azure Cosmos DB accounts using key-based authentication instead of Microsoft Entra IDEntra IDMicrosoft's cloud-based identity and access management service, formerly Azure Active Directory, used by cyber tools to authenticate users and enforce access policies in Microsoft 365 and Azure environments. only.
Adds Distributed Table Encrypted With Provider Managed Key Insight to identify Azure Cosmos DB accounts using service-managed rather than customer-managed keys.
Adds Distributed Table Without Network Traffic Restrictions Insight to identify Azure Cosmos DB accounts with unrestricted network access or 0.0.0.0 in firewall rules.
Adds Database Instance Without Microsoft Entra-Only Authentication (MySQL) Insight to identify Azure Database for MySQL Flexible Servers lacking Entra-only authentication.
Adds Database Instance Without Private Endpoint (MySQL Flexible Server) Insight to identify Azure Database for MySQL Flexible Servers without private endpoints.
Adds PostgreSQL Database Instance With Public Network Access Enabled Insight to identify PostgreSQL instances with public network access enabled.
Adds PostgreSQL Database Instance Without Private Endpoint Connection Insight to identify Azure Database for PostgreSQL Flexible Servers without a private endpoint connection.
Adds Database Instance Firewall Allows Public Ingress (SQL Server) Insight to flag SQL Server instances with a firewall rule permitting public ingress (start IP 0.0.0.0, end IP anything other than 0.0.0.0).
Prowler 5.43.0 replaces the pilot FedRAMP 20xFedRAMP 20xA GSA-led overhaul of the FedRAMP cloud-authorization program aimed at cutting compliance burden through continuous, automated evidence collection rather than point-in-time audits, letting vendors reach federal markets faster. frameworks with two unified 2026 frameworks, adds seven new AWS Inspector/FIPSFIPSA set of US federal standards published by NIST that define approved cryptographic algorithms and modules; cyber tools use it to meet compliance requirements in government and regulated environments. checks with supporting IAMIAMIdentity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access. permissions, and rounds out Private Cloud with self-registration control, external provider onboarding, AWS GovCloud failover, and invitation-management fixes.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.
Prowler 5.43.0 replaces the pilot FedRAMP 20xFedRAMP 20xA GSA-led overhaul of the FedRAMP cloud-authorization program aimed at cutting compliance burden through continuous, automated evidence collection rather than point-in-time audits, letting vendors reach federal markets faster. frameworks with two unified 2026 frameworks, adds seven new AWS Inspector/FIPSFIPSA set of US federal standards published by NIST that define approved cryptographic algorithms and modules; cyber tools use it to meet compliance requirements in government and regulated environments. checks with supporting IAMIAMIdentity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access. permissions, and rounds out Private Cloud with self-registration control, external provider onboarding, AWS GovCloud failover, and invitation-management fixes.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
8 FEATURES3 OF 8 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Seven new AWS Inspector and FIPS checksnew90how completely this was documenteddepth35/40specificity30/30actionability25/3090 / 100
Adds inspector2_coverage_scan_status_active, inspector2_coverage_recently_scanned (configurable via inspector2_max_days_since_last_scan, default 3), inspector2_active_findings_no_known_exploited_vulnerabilities, inspector2_active_findings_kev_within_due_date, inspector2_active_findings_within_max_age (configurable via inspector2_active_finding_max_age_days, default 192), elbv2_listener_fips_tls_enabled, and transfer_server_fips_security_policy_enabled.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Also adds inspector2:BatchGetFindingDetails to the Prowler additions policy and CloudFormationCloudFormationAn AWS service that lets you describe and provision cloud infrastructure as declarative YAML or JSON templates, so a cyber tool can reproducibly spin up or tear down its entire AWS environment with a single API call. scan role so the KEVKEVCISA's Known Exploited Vulnerabilities catalog, a list of vulnerabilities with evidence of exploitation in real attacks. It helps teams prioritize fixes for problems attackers already use. checks can pull CISA Known Exploited Vulnerability data directly from Inspector without an external feed; a missing permission now reports MANUAL instead of a false FAIL.
— names every check, config key, default, and IAM permission5.43.0
0201
FedRAMP 20x 2026 compliance frameworksbreaking85how completely this was documenteddepth35/40specificity30/30actionability20/3085 / 100
Adds fedramp_20x_ksi_2026, a universal compliance framework covering the 46 FedRAMPFedRAMPA US government program that standardizes cloud security authorization, letting vendors get a single assessment accepted across federal agencies instead of repeating the process for each one. Key Security Indicators across AWS, Azure, GCP, Kubernetes, and M365 from a single definition, and fedramp_20x_frr_class_c_2026, covering 158 FedRAMP Class C provider rules across the same providers. These replace the pilot per-provider frameworks fedramp_20x_ksi_low_aws, fedramp_20x_ksi_low_azure, and fedramp_20x_ksi_low_gcp; any automation or stored results referencing the pilot IDs must be updated.
— names frameworks and counts; migration path stated but not exact steps5.43.0
0302
Self-registration toggle for Private Cloudnew75how completely this was documenteddepth25/40specificity25/30actionability25/3075 / 100
Adds UI_SELF_REGISTRATION_ENABLED environment variable for Prowler Private Cloud deployments; set to false to make sign-up invitation-only, hiding the Sign up link and Create organization option.
— exact env var and behaviour, no rollout scope given5.43.0
0400
AWS partition bootstrap failover for GovCloudnew75how completely this was documenteddepth30/40specificity25/30actionability20/3075 / 100
When PROWLER_AWS_PARTITION is set, bootstrap STSSTSAWS Security Token Service, an Amazon Web Services API that issues short-lived credentials for IAM roles, letting cyber tools authenticate to AWS without storing long-term secrets. calls now try up to two additional regions in the partition on connection errors or timeouts, so GovCloud scans succeed on networks that route only to one regional endpoint.
— named env var and mechanism, no exact region list5.43.0
0500
Public endpoint signing for report downloadsnew67how completely this was documenteddepth25/40specificity20/30actionability22/3067 / 100
Adds DJANGO_OUTPUT_S3_AWS_PUBLIC_ENDPOINT_URL environment variable to sign report download URLs against a browser-reachable storage host, enabling downloads on deployments where object storage is only reachable inside the container network.
— named env var with clear use case, no example given5.43.0
0600
Invitation lifecycle fixesimproved65how completely this was documenteddepth25/40specificity22/30actionability18/3065 / 100
Expired invitations are now re-invitable: a pending invitation past its expiry is marked expired and a new invitation is created for the same email rather than returning a generic error; filter[state__in] on the invitations endpoint no longer returns a server error.
— names endpoint filter and before/after behaviour5.43.0
thinner coverage below
0703
SMN topic subscription check for Huawei Cloudnew45how completely this was documenteddepth15/40specificity15/30actionability15/3045 / 100
Adds smn_topic_subscriptions check for Huawei Cloud, reporting SMN topics that have no subscriptions configured.
— single check named but described only briefly5.43.0
0800
Registry marketplace and external provider onboardingnew42how completely this was documenteddepth20/40specificity12/30actionability10/3042 / 100
Adds registry marketplace and external provider onboarding for Private Cloud, with permission-based access, schema-driven credentials, connection checks, and scan launch.
— described only in prose, no named endpoints or config5.43.0
└──▷ BREAKING ON UPGRADE
!
The pilot framework IDs fedramp_20x_ksi_low_aws, fedramp_20x_ksi_low_azure, and fedramp_20x_ksi_low_gcp are replaced by fedramp_20x_ksi_2026; any automation or stored results referencing the pilot IDs must be updated.
Prowler 5.43.0 adds FedRAMP 20xFedRAMP 20xA GSA-led overhaul of the FedRAMP cloud-authorization program aimed at cutting compliance burden through continuous, automated evidence collection rather than point-in-time audits, letting vendors reach federal markets faster. 2026 frameworks, seven AWS Inspector/FIPSFIPSA set of US federal standards published by NIST that define approved cryptographic algorithms and modules; cyber tools use it to meet compliance requirements in government and regulated environments. checks, partition failover, and a self-registration toggle︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ GET THIS VERSION
$ git clone --branch 5.43.0 https://github.com/prowler-cloud/prowler.git
# already have the repo? check out this version:$ git checkout 5.43.0
Adds fedramp_20x_ksi_2026 universal compliance framework covering the 46 FedRAMPFedRAMPA US government program that standardizes cloud security authorization, letting vendors get a single assessment accepted across federal agencies instead of repeating the process for each one. Key Security Indicators across AWS, Azure, GCP, Kubernetes, and M365 from a single definition, replacing the pilot per-provider frameworks.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds fedramp_20x_frr_class_c_2026 universal compliance framework covering 158 FedRAMP Class C provider rules across AWS, Azure, GCP, Kubernetes, and M365.
Adds seven new AWS checks: inspector2_coverage_scan_status_active, inspector2_coverage_recently_scanned (configurable via inspector2_max_days_since_last_scan, default 3), inspector2_active_findings_no_known_exploited_vulnerabilities, inspector2_active_findings_kev_within_due_date, inspector2_active_findings_within_max_age (configurable via inspector2_active_finding_max_age_days, default 192), elbv2_listener_fips_tls_enabled, and transfer_server_fips_security_policy_enabled.
Adds inspector2:BatchGetFindingDetails to the Prowler additions policy and CloudFormationCloudFormationAn AWS service that lets you describe and provision cloud infrastructure as declarative YAML or JSON templates, so a cyber tool can reproducibly spin up or tear down its entire AWS environment with a single API call. scan role so KEVKEVCISA's Known Exploited Vulnerabilities catalog, a list of vulnerabilities with evidence of exploitation in real attacks. It helps teams prioritize fixes for problems attackers already use. checks can pull CISA Known Exploited Vulnerability data directly from Inspector without an external feed; missing permission reports MANUAL instead of a false FAIL.
Adds UI_SELF_REGISTRATION_ENABLED environment variable for Prowler Private Cloud deployments; set to false to make sign-up invitation-only, hiding the Sign up link and Create organization option.
+5 moreshow less
Adds DJANGO_OUTPUT_S3_AWS_PUBLIC_ENDPOINT_URL environment variable to sign report download URLs against a browser-reachable storage host, enabling downloads on deployments where object storage is only reachable inside the container network.
Adds smn_topic_subscriptions check for Huawei Cloud, reporting SMN topics that have no subscriptions configured.
Adds AWS partition bootstrap failover: when PROWLER_AWS_PARTITION is set, bootstrap STSSTSAWS Security Token Service, an Amazon Web Services API that issues short-lived credentials for IAM roles, letting cyber tools authenticate to AWS without storing long-term secrets. calls try up to two additional regions in the partition on connection errors or timeouts, so GovCloud scans succeed on networks that route only to one regional endpoint.
Adds registry marketplace and external provider onboarding for Private Cloud, with permission-based access, schema-driven credentials, connection checks, and scan launch.
Expired invitations are now re-invitable: a pending invitation past its expiry is marked expired and a new invitation is created for the same email rather than returning a generic error; filter[state__in] on the invitations endpoint no longer returns a server error.
Adds fedramp_20x_ksi_2026 universal compliance framework covering the 46 FedRAMPFedRAMPA US government program that standardizes cloud security authorization, letting vendors get a single assessment accepted across federal agencies instead of repeating the process for each one. Key Security Indicators across AWS, Azure, GCP, Kubernetes, and M365 from a single definition, replacing the pilot per-provider frameworks.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds fedramp_20x_frr_class_c_2026 universal compliance framework covering 158 FedRAMP Class C provider rules across AWS, Azure, GCP, Kubernetes, and M365.
Adds seven new AWS checks: inspector2_coverage_scan_status_active, inspector2_coverage_recently_scanned (configurable via inspector2_max_days_since_last_scan, default 3), inspector2_active_findings_no_known_exploited_vulnerabilities, inspector2_active_findings_kev_within_due_date, inspector2_active_findings_within_max_age (configurable via inspector2_active_finding_max_age_days, default 192), elbv2_listener_fips_tls_enabled, and transfer_server_fips_security_policy_enabled.
Adds UI_SELF_REGISTRATION_ENABLED environment variable for Prowler Private Cloud deployments; set to false to make sign-up invitation-only, hiding the Sign up link and Create organization option.
Adds DJANGO_OUTPUT_S3_AWS_PUBLIC_ENDPOINT_URL environment variable to sign report download URLs against a browser-reachable storage host, enabling downloads on deployments where object storage is only reachable inside the container network.
+2 moreshow less
Adds smn_topic_subscriptions check for Huawei Cloud, reporting SMN topics that have no subscriptions configured.
Adds registry marketplace and external provider onboarding for Private Cloud, with permission-based access, schema-driven credentials, connection checks, and scan launch.
3 more in Everything
└──▷ BREAKING ON UPGRADE
!The pilot framework IDs fedramp_20x_ksi_low_aws, fedramp_20x_ksi_low_azure, and fedramp_20x_ksi_low_gcp are replaced by fedramp_20x_ksi_2026; any automation or stored results referencing the pilot IDs must be updated.
Wiz is a cloud security platform that identifies and prioritizes vulnerabilities and risks across cloud infrastructure and applications.
Wiz shipped a GA WIN partners endpoint in its MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. server, letting partner AI agents pull live tenant context on demand during investigations.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
1 FEATURE1 OF 1 FEATUREmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0101
GA WIN partners endpoint for MCP agent integrationsnew70how completely this was documenteddepth30/40specificity25/30actionability15/3070 / 100
Wiz added a GA WIN (Wiz Integration Network) partners endpoint in the Wiz MCP, letting partner AI agents — Claude Code, Cursor, GitHub Copilot, or any remote-MCP-capable agent — search WIN documentation, retrieve API operations and required scopes, and query demo environment data without manual API calls.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ This introduces MCP-based agent integrations in WIN that let partner agents pull live Wiz context — Issues, Findings, affected resources, attack pathsattack pathsA possible sequence of steps an attacker could take to reach a valuable target. It connects weaknesses, permissions and reachable systems rather than treating each finding separately., and blast radius — directly from customer tenants on demand during investigations.
— Names the endpoint and agents but no method, path, or exact config.2026-09-22-55728d69
Wiz MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. gains a GA WIN partners endpoint so partner AI agents can pull live Issues, Findings, and resources on demand.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds a GA WIN partners endpoint in the Wiz MCP, letting partner AI agents (Claude Code, Cursor, GitHub Copilot, or any remote-MCP-capable agent) search WIN documentation, retrieve API operations and required scopes, and query demo environment data without manual API calls.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Introduces MCP-based agent integrations in the Wiz Integration Network (WIN), enabling partner AI agents to pull live Wiz context — Issues, Findings, affected resources, attack pathsattack pathsA possible sequence of steps an attacker could take to reach a valuable target. It connects weaknesses, permissions and reachable systems rather than treating each finding separately., and blast radius — directly from customer tenants on demand during investigations.
Chainguard provides trusted open source artifacts for every layer of your modern software stack—containers, language libraries, and VM images.
Chainguard launched a beta for storing and serving artifacts from an EU region, added eleven new container images across application, FIPSFIPSA set of US federal standards published by NIST that define approved cryptographic algorithms and modules; cyber tools use it to meet compliance requirements in government and regulated environments., base and commercial tiers, and flagged a breaking default-user change in the sonar-scanner-cli image that alters its working directory.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
3 FEATURES1 OF 3 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Default-user change breaks sonar-scanner-cli working directorybreaking75how completely this was documenteddepth25/40specificity25/30actionability25/3075 / 100
An October 12 default-user change in the sonar-scanner-cli image alters where the tool resolves its working directory, requiring pipelines to explicitly pass -Dsonar.working.directory=/usr/src/.scannerwork -Dsonar.projectBaseDir=/usr/src (e.g.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ docker run --rm -v "$(pwd):/usr/src" cgr.dev/chainguard/sonar-scanner-cli -Dsonar.working.directory=/usr/src/.scannerwork -Dsonar.projectBaseDir=/usr/src) to preserve existing behavior.
Preserve existing sonar-scanner-cli pipeline behavior after the October 12 default-user change by explicitly redirecting the working directory back to the project workspace.
$ docker run --rm-v "$(pwd):/usr/src" cgr.dev/chainguard/sonar-scanner-cli -Dsonar.working.directory=/usr/src/.scannerwork-Dsonar.projectBaseDir=/usr/src
— Gives exact runnable command and flags to work around the changechangelog-20260922-054520ad
0201
Sovereign Artifacts beta for EU data residencynew65how completely this was documenteddepth30/40specificity25/30actionability10/3065 / 100
Chainguard launched a Sovereign Artifacts beta that stores and serves Chainguard Containers and Chainguard Libraries artifact bytes in an EU region for enrolled customers, with automatic backfill of existing artifacts and approximately 30% faster pulls from Europe.
— Describes mechanism and benefit but no enrollment steps givenWeek of 2026-09-21
thinner coverage below
0300
New container images across tiersnew57how completely this was documenteddepth15/40specificity30/30actionability12/3057 / 100
Eleven new container images were added: cursor-agent (application tier), chainguard-desktop-workstation-pc (base tier), commercial-avocado (commercial tier), rustfs (application tier), cloudzero-agent (application + FIPS tier), trivy-k8s-wrapper (application + FIPS tier), access-log-exporter (application + FIPS tier), datahub-gms (application + FIPS tier), kates-connect (application + FIPS tier), kubeflow-trainer-controller-manager (application + FIPS tier), and tracee (application + FIPS tier).
— Names every image and tier but no pull commands or usage detailWeek of 2026-09-21
Chainguard adds EU Sovereign Artifacts beta for data residency and ships 18 new container images including FIPSFIPSA set of US federal standards published by NIST that define approved cryptographic algorithms and modules; cyber tools use it to meet compliance requirements in government and regulated environments. variants.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Launches Sovereign Artifacts beta, storing and serving Chainguard Containers and Chainguard Libraries artifact bytes in an EU region for enrolled customers, with automatic backfill of existing artifacts and approximately 30% faster pulls from Europe.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds new cursor-agent (application tier) container image.
Adds new chainguard-desktop-workstation-pc (base tier) container image.
Adds new commercial-avocado (commercial tier) container image.
Adds new rustfs (application tier) container image.
+7 moreshow less
Adds new cloudzero-agent (application + FIPS tier) container image.
Adds new trivy-k8s-wrapper (application + FIPS tier) container image.
Adds new access-log-exporter (application + FIPS tier) container image.
Adds new datahub-gms (application + FIPS tier) container image.
Adds new kates-connect (application + FIPS tier) container image.
Adds new kubeflow-trainer-controller-manager (application + FIPS tier) container image.
Adds new tracee (application + FIPS tier) container image.
Anchore's software supply chain solutions automate vulnerability scanning, strengthen container security, and support compliance with NIST, FedRAMP & more.
Anchore Enterprise v6.2 extends supply chain security into AI/ML models with native model artifact detection, an MCP ServerMCP ServerA process that exposes tools, resources, and prompts over Anthropic's Model Context Protocol, letting an AI agent call external APIs or local services through a standardised interface. for AI agent integration, VEXVEXA machine-readable statement from a vendor saying whether a CVE in a component actually affects their product. It is how a scanner is told to stop flagging a vulnerability that is not reachable.-aware policy suppression, and local SBOMSBOMA software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. generation during scanning.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
6 FEATURES3 OF 6 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0101
VEX-aware policy evaluationnew70how completely this was documenteddepth30/40specificity25/30actionability15/3070 / 100
Policies now support VEX annotations, automatically factoring in VEX status values such as not_affected or fixed to suppress false positives and prevent unnecessary build breaks.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Anchore Enterprise MCP Servernew65how completely this was documenteddepth25/40specificity25/30actionability15/3065 / 100
A new lightweight container image, the Anchore Enterprise MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Server, gives AI agents and tools direct, structured access to vulnerability findings, policy evaluation results, and SBOM catalog data without custom API integration scripts.
AI/ML model artifact detection in SBOM catalognew60how completely this was documenteddepth30/40specificity20/30actionability10/3060 / 100
Anchore now natively inspects container images for AI/ML model artifacts, including GGUFGGUFThe single-file model format used by llama.cpp and Ollama, holding the weights, usually quantized, together with the tokenizer and settings needed to run the model locally. files and Docker Model structures, indexing them as packages in the central SBOM catalog alongside traditional software components.
Local SBOM generation during scanningnew55how completely this was documenteddepth25/40specificity15/30actionability15/3055 / 100
Anchore now supports local SBOM generation and output during image scanning workflows, letting developers inspect component inventories and compliance status before pushing artifacts to central registries.
Severity-based package filteringnew50how completely this was documenteddepth20/40specificity15/30actionability15/3050 / 100
Packages within an application version can now be filtered by associated vulnerability severity (Critical, High, Medium) to accelerate targeted remediation.
Policy outcome change notificationsnew40how completely this was documenteddepth20/40specificity10/30actionability10/3040 / 100
Automated notifications now trigger whenever a policy outcome changes at the application version level, alerting security teams when a previously compliant artifact becomes non-compliant.
Anchore Enterprise v6.2 adds AI/ML model SBOMSBOMA software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. detection, MCP ServerMCP ServerA process that exposes tools, resources, and prompts over Anthropic's Model Context Protocol, letting an AI agent call external APIs or local services through a standardised interface. for agent integration, VEXVEXA machine-readable statement from a vendor saying whether a CVE in a component actually affects their product. It is how a scanner is told to stop flagging a vulnerability that is not reachable.-aware policies, and local SBOM generation.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Natively inspects container images for AI/ML model artifacts, including GGUFGGUFThe single-file model format used by llama.cpp and Ollama, holding the weights, usually quantized, together with the tokenizer and settings needed to run the model locally. files and Docker Model structures, indexing them as packages in the central SBOM catalog alongside traditional software components.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Introduces the Anchore Enterprise MCP Server, a lightweight container image that gives AI agents and tools direct, structured access to vulnerability findings, policy evaluation results, and SBOM catalog data without custom API integration scripts.
Adds policy support for VEX annotations, allowing policies to automatically factor in VEX status values such as not_affected or fixed to suppress false positives and prevent unnecessary build breaks.
Triggers automated notifications whenever a policy outcome changes at the application version level, alerting security teams when a previously compliant artifact becomes non-compliant.
Enables filtering of packages within an application version by associated vulnerability severity (Critical, High, Medium) to accelerate targeted remediation.
+1 moreshow less
Supports local SBOM generation and output during image scanning workflows, enabling developers to inspect component inventories and compliance status before pushing artifacts to central registries.
Natively inspects container images for AI/ML model artifacts, including GGUFGGUFThe single-file model format used by llama.cpp and Ollama, holding the weights, usually quantized, together with the tokenizer and settings needed to run the model locally. files and Docker Model structures, indexing them as packages in the central SBOM catalog alongside traditional software components.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Introduces the Anchore Enterprise MCP Server, a lightweight container image that gives AI agents and tools direct, structured access to vulnerability findings, policy evaluation results, and SBOM catalog data without custom API integration scripts.
Triggers automated notifications whenever a policy outcome changes at the application version level, alerting security teams when a previously compliant artifact becomes non-compliant.
Enables filtering of packages within an application version by associated vulnerability severity (Critical, High, Medium) to accelerate targeted remediation.
Datadog Cloud SIEM detects and investigates security threats across cloud infrastructure using logs, metrics, and threat intelligence.
Datadog Cloud SIEM's biggest addition this window is Dynamic Severity rules with fine-grained access controls, alongside new suppression rules, below-threshold detection logic, and three new out-of-the-box integrations.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
6 FEATURES0 OF 6 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Dynamic Severity rules for signalsnew75how completely this was documenteddepth30/40specificity20/30actionability25/3075 / 100
Cloud SIEM adds Dynamic Severity rules that adjust the severity of security signals based on the assets they affect, with customizable severity levels, custom tags, and rule-scoped isolation.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Access to these rules can be restricted with role-, team-, and user-level controls, requiring at least one editor role the current user belongs to before saving — done from the rule list's vertical three-dot menu via Restrict access.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Scope a Dynamic Severity rule's edit access to specific roles or teams so only authorized staff can modify signal severity adjustments.
📍In Cloud SIEM, open the Dynamic Severity rule list, click the vertical three-dot menu for the rule, select Restrict access, and use the dropdown to add one or more roles, teams, or users — ensuring your own role is included before saving.
Datadog Cloud SIEM adds Dynamic Severity rules, Env Remapping, Code Channels in Slack, and Data Access Control for signals.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
Scope a Dynamic Severity rule's edit access to specific roles or teams so only authorized staff can modify signal severity adjustments.
📍In Cloud SIEM, open the Dynamic Severity rule list, click the vertical three-dot menu for the rule, select Restrict access, and use the dropdown to add one or more roles, teams, or users — ensuring your own role is included before saving.
Adds Dynamic Severity rules to adjust the severity of security signals based on the assets they affect, with customizable severity levels, custom tags, and rule-scoped isolation.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds role-, team-, and user-level access controls for Dynamic Severity rules, requiring at least one editor role the current user belongs to before saving.
Adds out-of-the-box integrations for Palo Alto Networks Firewall, Windows Event Logs, and Wiz.
Adds New Suppression rules for Cloud SIEM detections.
+2 moreshow less
Improves Bits Investigation accuracy.
Adds below-threshold (a < N and a <= 0) detection cases to Threshold detection rules alongside the existing above-threshold (a > N) case.
Adds Dynamic Severity rules to adjust the severity of security signals based on the assets they affect, with customizable severity levels, custom tags, and rule-scoped isolation.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds role-, team-, and user-level access controls for Dynamic Severity rules, requiring at least one editor role the current user belongs to before saving.
Databricks is a unified analytics platform for data engineering, data science, and machine learning built on Apache Spark.
Databricks shipped automatic sensitive-data classification in Unity Catalog, a GA account-wide query history system table, and a new Databricks Runtime 19 with SQL/DataFrame functions, session-scoped Python UDF env vars, and improved shuffle defaults, alongside expanded ABACABACAttribute-based access control, where rules evaluate facts about the user, resource and request. Access can depend on conditions such as department, data sensitivity or device status. column mask coverage for VARIANT types.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
4 FEATURES0 OF 4 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Databricks Runtime 19 SQL/DataFrame functions and Python UDF env varsnew93how completely this was documenteddepth35/40specificity28/30actionability30/3093 / 100
Databricks Runtime 19 adds the truncate function to SQL, Scala DataFrame, and Python DataFrame APIs to truncate a number to a specified scale without rounding, and trim_array to remove elements from the end (positive count) or beginning (negative count) of an array.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ It also adds the spark.pythonWorkerEnv.<variable-name> configuration prefix to set session-scoped environment variables for Python UDF scalar worker processes, and enables auto-optimized shuffle v2 by default for workloads that do not set a fixed shuffle partition count.
Inject a custom environment variable (e.g. a secret path) into every Python UDF worker in a session without restarting the cluster.
Query history system table generally availableimproved70how completely this was documenteddepth25/40specificity25/30actionability20/3070 / 100
The system.query.history system table is now GA, providing account-wide records of SQL warehouse and serverless compute executions, including execution status, duration metrics, and query source.
ABAC column masks extend VARIANT casts to ARRAY and MAPimproved60how completely this was documenteddepth25/40specificity25/30actionability10/3060 / 100
VARIANT cast support in ABAC column masks now extends to ARRAY and MAP column types, in addition to previously supported STRUCT and other types, requiring Databricks Runtime 19 or above.
Truncate a monetary amount to 2 decimal places without rounding, useful for audit-safe financial calculations.
$ SELECT truncate(price, 2) AS truncated_price FROM transactions;
Drop the last N elements from an array column to trim trailing nulls or sentinel values before aggregation.
$ SELECT trim_array(tags, 2) AS trimmed_tags FROM events;
Adds spark.pythonWorkerEnv.<variable-name> configuration prefix to set session-scoped environment variables for Python UDF scalar worker processes.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds truncate function to SQL, Scala DataFrame, and Python DataFrame APIs to truncate a number to a specified scale without rounding.
Adds trim_array function to SQL, Scala DataFrame, and Python DataFrame APIs to remove elements from the end of an array (positive count) or the beginning (negative count).
Enables auto-optimized shuffle v2 by default for workloads that do not set a fixed shuffle partition count.
Adds spark.pythonWorkerEnv.<variable-name> configuration prefix to set session-scoped environment variables for Python UDF scalar worker processes.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds truncate function to SQL, Scala DataFrame, and Python DataFrame APIs to truncate a number to a specified scale without rounding.
Adds trim_array function to SQL, Scala DataFrame, and Python DataFrame APIs to remove elements from the end of an array (positive count) or the beginning (negative count).
VARIANT column masks in ABACABACAttribute-based access control, where rules evaluate facts about the user, resource and request. Access can depend on conditions such as department, data sensitivity or device status. now cover ARRAY and MAP types alongside STRUCT, requiring Databricks Runtime 19+.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Tines lets teams put AI to work across their most sensitive systems, data, and processes, with the security and governance to do it safely.
Tines 43.3.0 brings deeper case management into the storyboard, adding change tracking, formula-driven fields, and visual case creation.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
1 FEATURE0 OF 1 FEATUREmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Case tracking, formulas, and visual creation in storyboardnew40how completely this was documenteddepth15/40specificity15/30actionability10/3040 / 100
Tines now adds change control tracking for cases directly within the storyboard, formula support for case details fields, and the ability to create cases visually from within the storyboard.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Give feedback to the Huntress team so we can make more informed product decisions. Powered by Canny.
Huntress shipped Defender scan toggles for Managed Antivirus, macOS parity on the agent overview page, a new detection for a disclosed Screen Sharing exploit, and two Shadow Workflow hardening controls in Managed ISPMISPMIdentity Security Posture Management: a discipline for continuously discovering, assessing, and remediating identity-related risks across users, accounts, and entitlements, giving cyber tools a unified view of identity exposure..︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
4 FEATURES0 OF 4 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Shadow Workflow hardening controls in Managed ISPMnew83how completely this was documenteddepth30/40specificity28/30actionability25/3083 / 100
Managed ISPM adds two new M365 security controls targeting Shadow Workflows: Ensure Direct Send is disabled for Microsoft Exchange Online, and Tenant Allow/Block list should contain zero entries in the allow list for Microsoft Defender for Office 365.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Both controls can be scheduled for deployment via the Schedule for Deployment option rather than Managed Deployments to avoid unplanned end-user impact.
Schedule the Exchange Online Shadow Workflow hardening controls to roll out to tenants without auto-deploying to avoid unplanned end-user impact.
📍In the Huntress console, open the Microsoft 365 hardening controls, locate Ensure Direct Send is disabled and 'Tenant Allow/Block list should contain zero entries in the allow list', and use the Schedule for Deployment option rather than Managed Deployments.
Network and Archive File Scanning toggles for Defendernew72how completely this was documenteddepth22/40specificity25/30actionability25/3072 / 100
Managed Antivirus now exposes Network File Scanning and Archive File Scanning toggles for Microsoft Defender, found under EDREDREndpoint detection and response, monitoring computers for suspicious behavior and providing investigation and response controls, such as isolating a device. > Managed Antivirus > Defender Configuration > Scans.
Enable Archive File Scanning and explicitly disable Network File Scanning for Defender to harden malware-in-ZIP detection without impacting shared-drive performance.
📍In the Huntress console, go to EDR › Managed Antivirus › Defender Configuration › Scans, set Network File Scanning to Off and Archive File Scanning to On, then save.
Detection for macOS Screen Sharing root exploitnew50how completely this was documenteddepth25/40specificity20/30actionability5/3050 / 100
A new detection fires when a Screen Sharing session attaches to a root user via a legacy authentication handshake, covering an unauthenticated file-read flaw in Apple's Screen Sharing service disclosed July 2026.
macOS last logged-in user on agent overviewimproved43how completely this was documenteddepth20/40specificity15/30actionability8/3043 / 100
The agent overview page now shows the last logged-in user for macOS endpoints, a field previously available only for Windows, requiring Agent v0.14.196 or later.
Huntress adds macOS Screen Sharing visibility, quarantine-strip detections, and Defender scan toggle controls for M365 and endpoint hardening.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
Enable Archive File Scanning and explicitly disable Network File Scanning for Defender to harden malware-in-ZIP detection without impacting shared-drive performance.
📍In the Huntress console, go to EDR › Managed Antivirus › Defender Configuration › Scans, set Network File Scanning to Off and Archive File Scanning to On, then save.
Schedule the Exchange Online Shadow Workflow hardening controls to roll out to tenants without auto-deploying to avoid unplanned end-user impact.
📍In the Huntress console, open the Microsoft 365 hardening controls, locate Ensure Direct Send is disabled and 'Tenant Allow/Block list should contain zero entries in the allow list', and use the Schedule for Deployment option rather than Managed Deployments.
Adds Network File Scanning and Archive File Scanning toggles for Microsoft Defender in Managed Antivirus, found under EDREDREndpoint detection and response, monitoring computers for suspicious behavior and providing investigation and response controls, such as isolating a device. > Managed Antivirus > Defender Configuration > Scans.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Extends the agent overview page to show the last logged-in user for macOS endpoints (previously Windows-only), requiring Agent v0.14.196 or later.
Adds a detection that fires when a Screen Sharing session attaches to a root user via a legacy authentication handshake, covering an unauthenticated file-read flaw in Apple's Screen Sharing service disclosed July 2026.
Adds Network File Scanning and Archive File Scanning toggles for Microsoft Defender in Managed Antivirus, found under EDREDREndpoint detection and response, monitoring computers for suspicious behavior and providing investigation and response controls, such as isolating a device. > Managed Antivirus > Defender Configuration > Scans.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds a detection that fires when a Screen Sharing session attaches to a root user via a legacy authentication handshake, covering an unauthenticated file-read flaw in Apple's Screen Sharing service disclosed July 2026.
Huntress Managed ISPMISPMIdentity Security Posture Management: a discipline for continuously discovering, assessing, and remediating identity-related risks across users, accounts, and entitlements, giving cyber tools a unified view of identity exposure. adds two new M365 security controls targeting Shadow Workflows in Exchange Online and Defender for Office 365.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds Ensure Direct Send is disabled control for Microsoft Exchange Online, available to schedule for deployment in Managed ISPM.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds 'Tenant Allow/Block list should contain zero entries in the allow list' control for Microsoft Defender for Office 365, available to schedule for deployment in Managed ISPM.
Trend Vision One is Trend Micro's cloud-based XDR platform providing unified security visibility and threat detection across endpoints, networks, and cloud environments.
Trend Vision One's Service Gateway Smart Protection Services 2.0.11 release adds support for the TrendAI Vision One agent.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
1 FEATURE0 OF 1 FEATUREmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
TrendAI Vision One agent support on Service Gatewaynew30how completely this was documenteddepth10/40specificity15/30actionability5/3030 / 100
Service Gateway Smart Protection Services version 2.0.11 adds support for the TrendAI Vision One™ agent.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Fleet shipped a full Reports feature — scheduling, live queries, CSV export, label targeting and configurable result caps — alongside a broad 4.92.0 release that adds a cancelable Apple MDMMDMMobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies. command endpoint, per-platform disk encryption controls, Android and iOS MDM enhancements, and osquery config bandwidth-saving options, plus two breaking changes to log formatting and Windows profile resend behavior.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
20 FEATURES2 OF 20 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Reports feature with scheduling, live queries and CSV exportnew95how completely this was documenteddepth35/40specificity30/30actionability30/3095 / 100
Fleet adds a Reports section that lets admins create, schedule, run live, and export reports as CSV.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Storage is controlled via server_settings.report_cap (default 1,000 stored results per report) and server_settings.discard_reports_data globally, or per-report via the discard_data field on the create/update report API and per-report/global Store data toggles in Advanced options. schedule_splay_percent in agent options randomizes each host's check-in time (up to 10% by default) to spread load. Label-based host targeting (Fleet Premium) is available via a Custom target selector, a Manage automations bulk UI (admin-only) configures which reports send data to a log destination, and running SELECT * FROM osquery_schedule as a live query shows exactly when a host will next check in for a scheduled report.
Cap stored report results at 500 and disable global result persistence to protect database performance as you add more reports.
Spread scheduled report check-ins across a wider window to reduce simultaneous host load on a large fleet.
yaml
schedule_splay_percent: 20
— Names every config key, field and query; runnable examples givenproduct docs
0200
Osquery config bandwidth-saving optionsnew95how completely this was documenteddepth35/40specificity30/30actionability30/3095 / 100
Adds osquery.config_in_memory_cache to control an in-memory cache of the osquery config's scheduled-report section (disabled by default, set true to re-enable). Adds osquery.config_etags (env FLEET_OSQUERY_CONFIG_ETAGS, default off) to enable conditional request (etag) support on /api/osquery/config, returning a minimal {"etag":"ok"} response when config is unchanged. Adds osquery.redis_config_etags (env FLEET_OSQUERY_REDIS_CONFIG_ETAGS, default off, requires osquery.config_etags) to answer matching etag check-ins directly from a Redis-backed ETagETagAn HTTP response header that carries an opaque version token for a resource, letting clients skip re-downloading unchanged content by sending the token back in a conditional request. store, skipping config build and database reads entirely.
Reduce agent config bandwidth on large fleets by enabling etag-based conditional config responses so unchanged configs return only a minimal acknowledgement.
— Every config key and env var named with mechanism and examplefleet-v4.92.0
0300
Cancelable pending Apple MDM commandsnew90how completely this was documenteddepth30/40specificity30/30actionability30/3090 / 100
Adds DELETE /api/v1/fleet/hosts/:id/commands/:command_uuid to cancel a pending Apple MDM lock, wipe, clear passcode, or enable lost mode command before the host receives it.
Cancel a pending Apple MDM wipe before a host receives it — useful when a wipe was sent to the wrong device.
— Exact endpoint, method and runnable curl example providedfleet-v4.92.0
0400
Expanded Android host vitals collectionnew80how completely this was documenteddepth30/40specificity30/30actionability20/3080 / 100
Adds collection of additional Android host vitals — USB debugging, passcode set, Google Play Protect, encryption status, manufacturer, security update version, kernel and bootloader version, software update status, API level, security posture, and per-SIM phone numbers — returned by get host endpoints.
— Long named list of vitals but endpoint path not given exactlyfleet-v4.92.0
0500
SSO-required end user authentication for Fleet Desktopnew70how completely this was documenteddepth25/40specificity25/30actionability20/3070 / 100
Adds a new End user authentication setting (fleet_desktop.sso_enabled, Fleet Premium) requiring end users to sign in via SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. before accessing Fleet Desktop's My device page.
— Named config key and exact UI page it gatesfleet-v4.92.0
0600
Per-platform disk encryption enforcement and key escrownew65how completely this was documenteddepth25/40specificity25/30actionability15/3065 / 100
Adds per-platform disk encryption settings: enforcement and key escrow for macOS, enforcement for Windows, and key escrow for Linux.
— Scope per platform given but no config key or path namedfleet-v4.92.0
0700
Inactive user status and activity timestampsnew65how completely this was documenteddepth25/40specificity25/30actionability15/3065 / 100
Adds an Inactive status with tooltip to the Users table, with new last_login_at, last_activity_at, and server-computed status fields (active, inactive, or no_access) returned from the users API.
— Named fields and enum values but no example requestfleet-v4.92.0
0801
Human-readable duration fields in server logsbreaking65how completely this was documenteddepth25/40specificity20/30actionability20/3065 / 100
Duration fields in Fleet server logs (e.g. took) now render as human-readable strings with time units (e.g. "1.116187ms") instead of raw nanosecond numbers — log pipelines that parse these fields numerically must be updated.
— Exact field, before/after format, and migration note givenfleet-v4.92.0
0902
Windows user-scoped profiles not auto-resent after upgradebreaking65how completely this was documenteddepth25/40specificity20/30actionability20/3065 / 100
Windows user-scoped configuration profiles that already failed on an earlier Fleet version are not resent automatically after upgrading to 4.92.0 — admins must resend them once (or edit the profile) for Fleet to deliver them when a user is signed in.
— Clear before/after with an explicit remediation stepfleet-v4.92.0
1000
MDM enrollment fields on host API responsesnew60how completely this was documenteddepth20/40specificity25/30actionability15/3060 / 100
Adds mdm.is_personal_enrollment to host API responses, reporting whether the last MDM enrollment was personal (BYODBYODBring Your Own Device: a policy allowing employees to use personal phones, laptops, or tablets for work, creating a network of unmanaged endpoints that cyber tools must monitor or enforce policy on.) and persisting after unenrollment. Adds mdm.bootstrap_token_escrowed to the get host and get host by Fleet Desktop token API responses.
— Both API fields named but no request example givenfleet-v4.92.0
thinner coverage below
1100
CVSS severity filter on vulnerability exposure dashboardnew55how completely this was documenteddepth20/40specificity20/30actionability15/3055 / 100
Adds a severity (CVSSCVSSCommon Vulnerability Scoring System, a method for describing a vulnerability's characteristics and severity. Its score is not the probability that attackers will exploit it. score) filter to the Vulnerability exposure dashboard chart (Fleet Premium), with min/max score inputs appearing only when custom severity is selected.
— UI behaviour described but no exact navigation or API givenfleet-v4.92.0
1200
Per-endpoint max request body size overridenew50how completely this was documenteddepth15/40specificity20/30actionability15/3050 / 100
Adds server.endpoint_request_size_overrides configuration to set a max request body size per API endpoint.
— Config key named but no example or exact endpoints listedfleet-v4.92.0
1300
Experimental WebSocket notification transportnew50how completely this was documenteddepth15/40specificity20/30actionability15/3050 / 100
Adds websocket.transport_enabled server configuration to enable an experimental WebSocketWebSocketA protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output. notification transport for fleetd agents (disabled by default).
— Named config key but no usage detail beyond default statefleet-v4.92.0
1400
Automatic in-house app install on iOS/iPadOS enrollmentnew50how completely this was documenteddepth20/40specificity20/30actionability10/3050 / 100
Adds automatic installation of in-house apps (.ipa) on iOS and iPadOS hosts when they enroll into Fleet.
— Describes behaviour with format but no setup stepsfleet-v4.92.0
1500
Autopilot registry sync for pending Windows hostsnew50how completely this was documenteddepth20/40specificity20/30actionability10/3050 / 100
Adds Windows devices from a connected Microsoft Entra tenant's Autopilot registry to Fleet as pending hosts before enrollment.
— Mechanism named but no connection or config steps givenfleet-v4.92.0
1600
Resend configuration profile on policy automation failurenew40how completely this was documenteddepth15/40specificity15/30actionability10/3040 / 100
Adds support for resending a configuration profile on policy failure as part of a policy automation.
— Bare description, no config key or trigger detailfleet-v4.92.0
1700
QR code for host enrollment linknew40how completely this was documenteddepth10/40specificity15/30actionability15/3040 / 100
Adds a QR code for the enrollment link on the Android and iOS/iPadOS tabs of the Add hosts modal.
— Exact UI location named though feature itself is minorfleet-v4.92.0
1800
display_name for Fleet-maintained apps in GitOpsnew35how completely this was documenteddepth10/40specificity15/30actionability10/3035 / 100
Adds display_name support for Fleet-maintained apps in GitOpsGitOpsA practice where Git repositories serve as the single source of truth for infrastructure and application state, with automated systems continuously reconciling live environments to match what is declared in version control..
— Named field but no file path or usage shownfleet-v4.92.0
1900
Sort versions table by version on Software details pagenew30how completely this was documenteddepth10/40specificity10/30actionability10/3030 / 100
Adds the ability to sort the versions table by version on the Software details page.
— UI path named but feature is a minor sort togglefleet-v4.92.0
2000
Audit activity for unmatched SCIM deprovisioningnew25how completely this was documenteddepth10/40specificity10/30actionability5/3025 / 100
Adds an audit activity when a deprovisioned SCIMSCIMA standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave. user has no email to match a Fleet account.
— Bare description with no field or endpoint namedfleet-v4.92.0
└──▷ BREAKING ON UPGRADE
!
Duration fields in Fleet server logs (e.g. took) now render as human-readable strings with time units (e.g. "1.116187ms") instead of raw nanosecond numbers — log pipelines that parse these fields numerically must be updated.
!
Windows user-scoped configuration profiles that already failed on an earlier Fleet version are not resent automatically after upgrading — admins must resend them once (or edit the profile) for Fleet to deliver them when a user is signed in.
Fleet 4.92.0 adds Android MDMMDMMobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies. commands, per-platform disk encryption, cancelable Apple MDM commands, and new osquery bandwidth-saving config options.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ GET THIS VERSION
$ git clone --branch fleet-v4.92.0 https://github.com/fleetdm/fleet.git
# already have the repo? check out this version:$ git checkout fleet-v4.92.0
└──▷ USE IT
Reduce agent config bandwidth on large fleets by enabling etag-based conditional config responses so unchanged configs return only a minimal acknowledgement.
Adds osquery.config_in_memory_cache server configuration option to control the in-memory cache of the osquery config's scheduled-report section (set to true to re-enable; disabled by default).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds osquery.config_etags server option (FLEET_OSQUERY_CONFIG_ETAGS, default off) to enable conditional request (etag) support on /api/osquery/config, sending a minimal {"etag":"ok"} response to agents whose configuration is unchanged.
Adds osquery.redis_config_etags server option (FLEET_OSQUERY_REDIS_CONFIG_ETAGS, default off, requires osquery.config_etags) to answer matching etag check-ins directly from a Redis-backed ETagETagAn HTTP response header that carries an opaque version token for a resource, letting clients skip re-downloading unchanged content by sending the token back in a conditional request. store, skipping the config build and database reads entirely.
Adds server.endpoint_request_size_overrides configuration to set a max request body size per API endpoint.
Adds websocket.transport_enabled server configuration to enable an experimental WebSocketWebSocketA protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output. notification transport for fleetd agents (disabled by default).
+15 moreshow less
Adds mdm.is_personal_enrollment field to host API responses, reporting whether the last MDM enrollment was personal (BYODBYODBring Your Own Device: a policy allowing employees to use personal phones, laptops, or tablets for work, creating a network of unmanaged endpoints that cyber tools must monitor or enforce policy on.) and persisting after unenrollment.
Adds mdm.bootstrap_token_escrowed field to the get host and get host by Fleet Desktop token API responses.
Adds DELETE /api/v1/fleet/hosts/:id/commands/:command_uuid to cancel a pending Apple MDM lock, wipe, clear passcode, or enable lost mode command before the host receives it.
Adds per-platform disk encryption settings: enforcement and key escrow for macOS, enforcement for Windows, and key escrow for Linux.
Adds a new End user authentication setting (fleet_desktop.sso_enabled, Fleet Premium) requiring end users to sign in via SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. before accessing Fleet Desktop's My device page.
Adds a severity (CVSSCVSSCommon Vulnerability Scoring System, a method for describing a vulnerability's characteristics and severity. Its score is not the probability that attackers will exploit it. score) filter to the Vulnerability exposure dashboard chart (Fleet Premium), with min/max score inputs appearing only when custom severity is selected.
Adds collection of additional Android host vitals (USB debugging, passcode set, Google Play Protect, encryption status, manufacturer, security update version, kernel and bootloader version, software update status, API level, security posture, and per-SIM phone numbers) returned by get host endpoints.
Adds automatic installation of in-house apps (.ipa) on iOS and iPadOS hosts when they enroll into Fleet.
Adds Windows devices from a connected Microsoft Entra tenant's Autopilot registry to Fleet as pending hosts before enrollment.
Adds support for resending a configuration profile on policy failure as part of a policy automation.
Adds display_name support for Fleet-maintained apps in GitOpsGitOpsA practice where Git repositories serve as the single source of truth for infrastructure and application state, with automated systems continuously reconciling live environments to match what is declared in version control..
Adds a QR code for the enrollment link on the Android and iOS/iPadOS tabs of the Add hosts modal.
Adds an audit activity when a deprovisioned SCIMSCIMA standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave. user has no email to match a Fleet account.
Adds an Inactive status with tooltip to the Users table, with new last_login_at, last_activity_at, and server-computed status fields (active, inactive, or no_access) returned from the users API.
Adds the ability to sort the versions table by version on the Software details page.
Adds osquery.config_in_memory_cache server configuration option to control the in-memory cache of the osquery config's scheduled-report section (set to true to re-enable; disabled by default).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds osquery.config_etags server option (FLEET_OSQUERY_CONFIG_ETAGS, default off) to enable conditional request (etag) support on /api/osquery/config, sending a minimal {"etag":"ok"} response to agents whose configuration is unchanged.
Adds osquery.redis_config_etags server option (FLEET_OSQUERY_REDIS_CONFIG_ETAGS, default off, requires osquery.config_etags) to answer matching etag check-ins directly from a Redis-backed ETagETagAn HTTP response header that carries an opaque version token for a resource, letting clients skip re-downloading unchanged content by sending the token back in a conditional request. store, skipping the config build and database reads entirely.
Adds server.endpoint_request_size_overrides configuration to set a max request body size per API endpoint.
Adds websocket.transport_enabled server configuration to enable an experimental WebSocketWebSocketA protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output. notification transport for fleetd agents (disabled by default).
+11 moreshow less
Adds mdm.is_personal_enrollment field to host API responses, reporting whether the last MDM enrollment was personal (BYODBYODBring Your Own Device: a policy allowing employees to use personal phones, laptops, or tablets for work, creating a network of unmanaged endpoints that cyber tools must monitor or enforce policy on.) and persisting after unenrollment.
Adds mdm.bootstrap_token_escrowed field to the get host and get host by Fleet Desktop token API responses.
Adds DELETE /api/v1/fleet/hosts/:id/commands/:command_uuid to cancel a pending Apple MDM lock, wipe, clear passcode, or enable lost mode command before the host receives it.
Adds per-platform disk encryption settings: enforcement and key escrow for macOS, enforcement for Windows, and key escrow for Linux.
Adds a new End user authentication setting (fleet_desktop.sso_enabled, Fleet Premium) requiring end users to sign in via SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. before accessing Fleet Desktop's My device page.
Adds automatic installation of in-house apps (.ipa) on iOS and iPadOS hosts when they enroll into Fleet.
Adds Windows devices from a connected Microsoft Entra tenant's Autopilot registry to Fleet as pending hosts before enrollment.
Adds support for resending a configuration profile on policy failure as part of a policy automation.
Adds a QR code for the enrollment link on the Android and iOS/iPadOS tabs of the Add hosts modal.
Adds an audit activity when a deprovisioned SCIMSCIMA standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave. user has no email to match a Fleet account.
Adds an Inactive status with tooltip to the Users table, with new last_login_at, last_activity_at, and server-computed status fields (active, inactive, or no_access) returned from the users API.
4 more in Everything
└──▷ BREAKING ON UPGRADE
!Duration fields in Fleet server logs (e.g. took) now render as human-readable strings with time units (e.g. "1.116187ms") instead of raw nanosecond numbers — log pipelines that parse these fields numerically must be updated.
!Windows user-scoped configuration profiles that already failed on an earlier Fleet version are not resent automatically after upgrading — admins must resend them once (or edit the profile) for Fleet to deliver them when a user is signed in.
Manage devices and everything they touch. See how security, IT, and compliance get easier when unified around devices with Iru.
Iru added a Recommended privacy permissions area to its Privacy Library Item for iPhone and iPad, letting admins batch-configure app and Safari permissions into a single consent prompt.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
1 FEATURE0 OF 1 FEATUREmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Recommended privacy permissions for iPhone and iPadnew58how completely this was documenteddepth25/40specificity18/30actionability15/3058 / 100
A new Recommended privacy permissions area inside the Privacy Library Item lets admins specify app permissions and Safari website permissions that managed apps and sites require.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ End users see a single grouped consent prompt with Allow all or Not Now options instead of per-app popups.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
When onboarding managed iPhones, configure recommended permissions so users receive a single grouped consent prompt instead of per-app popups.
📍In the admin console, open the Privacy Library Item, navigate to the Recommended privacy permissions section for iPhone and iPad, add the required app permissions and Safari website permissions, then save and push to managed devices.
Iru's Privacy Library Item gains a Recommended privacy permissions area for iPhone and iPad, letting admins batch-prompt users for app and Safari permissions.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
When onboarding managed iPhones, configure recommended permissions so users receive a single grouped consent prompt instead of per-app popups.
📍In the admin console, open the Privacy Library Item, navigate to the Recommended privacy permissions section for iPhone and iPad, add the required app permissions and Safari website permissions, then save and push to managed devices.
MSTICPy 3.1.0 adds a new no-key threat-intelligence provider and Python 3.14 support, alongside two breaking changes to runtime dependencies and a user-agent header key.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
4 FEATURES2 OF 4 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0101
User-agent header key renamedbreaking75how completely this was documenteddepth25/40specificity25/30actionability25/3075 / 100
Code that directly indexes the dictionary returned by mp_ua_header() must replace ["UserAgent"] with ["User-Agent"]; code that passes the complete dictionary as HTTP headers does not need to change, and code needing the raw identifier can use MSTICPY_USER_AGENT.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
— Exact old/new key names and env var given, actionable migrationv3.1.0
0200
ScanMalware threat-intelligence providernew70how completely this was documenteddepth30/40specificity25/30actionability15/3070 / 100
Adds the ScanMalware TI provider, supporting verdict lookups for hosts and URLs, passive-DNS context for IP addresses, and quick query modes for bulk lookups. No API credentials are required to use it.
— Names provider, lookup types, and quick mode but no usage examplev3.1.0
thinner coverage below
0302
NumPy 1.x dropped from runtime requirementsbreaking45how completely this was documenteddepth15/40specificity15/30actionability15/3045 / 100
NumPy 1.x is no longer supported by the declared runtime requirements; users should review environment constraints for NumPy 2 compatibility before upgrading.
— Clear migration note but no version specificsv3.1.0
0400
Python 3.14 supportnew30how completely this was documenteddepth10/40specificity15/30actionability5/3030 / 100
Adds Python 3.14 to the supported package classifiers and CI test matrix.
— Bare compatibility note, no further detailv3.1.0
└──▷ BREAKING ON UPGRADE
!
NumPy 1.x is no longer supported by the declared runtime requirements — review environment constraints for NumPy 2 compatibility before upgrading.
!
Code that directly indexes the dictionary returned by mp_ua_header() must replace ["UserAgent"] with ["User-Agent"]; code that passes the complete dictionary as HTTP headers does not need to change, and code needing the raw identifier can use MSTICPY_USER_AGENT.
MSTICPy 3.1.0 adds a new ScanMalware TI provider for DNS, IP, and URL observables with no API key required.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ GET THIS VERSION
$ git clone --branch v3.1.0 https://github.com/microsoft/msticpy.git
# already have the repo? check out this version:$ git checkout v3.1.0
Adds the ScanMalware threat-intelligence provider supporting verdict lookups for hosts and URLs, passive-DNS context for IP addresses, and quick query modes for bulk lookups — no API credentials required.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds Python 3.14 to the supported package classifiers and CI test matrix.
Adds the ScanMalware threat-intelligence provider supporting verdict lookups for hosts and URLs, passive-DNS context for IP addresses, and quick query modes for bulk lookups — no API credentials required.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
1 more in Everything
└──▷ BREAKING ON UPGRADE
!NumPy 1.x is no longer supported by the declared runtime requirements — review environment constraints for NumPy 2 compatibility before upgrading.
!Code that directly indexes the dictionary returned by mp_ua_header() must replace ["UserAgent"] with ["User-Agent"]; code that passes the complete dictionary as HTTP headers does not need to change, and code needing the raw identifier can use MSTICPY_USER_AGENT.
OpenCTI's latest window adds new PrometheusPrometheusAn open-source monitoring system maintained by the CNCF that scrapes and stores time-series metrics, giving cyber tools a standard way to expose and query operational data. telemetry metrics, granular health-monitoring and usage-metrics manager configuration, Redis TLS SNIRedis TLS SNIA Redis feature that uses TLS Server Name Indication to route incoming connections to different TLS certificates or configurations based on the hostname the client declares at handshake time. support, and exponential back-off tuning for missing-reference retries, alongside product updates for Fintel reports, News Feed integrations, and user merge.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Open Cyber Threat Intelligence Platform
OpenCTI's latest window adds new PrometheusPrometheusAn open-source monitoring system maintained by the CNCF that scrapes and stores time-series metrics, giving cyber tools a standard way to expose and query operational data. telemetry metrics, granular health-monitoring and usage-metrics manager configuration, Redis TLS SNIRedis TLS SNIA Redis feature that uses TLS Server Name Indication to route incoming connections to different TLS certificates or configurations based on the hostname the client declares at handshake time. support, and exponential back-off tuning for missing-reference retries, alongside product updates for Fintel reports, News Feed integrations, and user merge.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
7 FEATURES0 OF 7 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Configurable health-monitoring and usage-metrics managernew95how completely this was documenteddepth35/40specificity30/30actionability30/3095 / 100
Adds app:health_monitoring:dependency_check_interval (APP__HEALTH_MONITORING__DEPENDENCY_CHECK_INTERVAL) to control how often dependency health checks run, in milliseconds, for ElasticSearch/OpenSearchOpenSearchAn open-source search and analytics engine, forked from Elasticsearch by AWS in 2021, that lets cyber tools store, query, and visualize large volumes of log or event data without licensing restrictions., S3/MinIO, RabbitMQ, and Redis, and app:health_monitoring:usage_metrics_interval (APP__HEALTH_MONITORING__USAGE_METRICS_INTERVAL) to control how often storage and ingestion usage metrics are collected and shared across the cluster via Redis, settable to 0 to disable collection.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds platform_usage_metrics_manager:enabled (PLATFORM_USAGE_METRICS_MANAGER__ENABLED) to toggle the manager that gathers these usage metrics, and platform_usage_metrics_manager:lock_key (PLATFORM_USAGE_METRICS_MANAGER__LOCK_KEY, default platform_usage_metrics_manager_lock) to control its distributed lock.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Set health monitoring refresh intervals so Prometheus scrapes never trigger live dependency probes — tune dependency checks and expensive usage scans independently.
Configure health-monitoring check cadence and enable the usage-metrics manager in a multi-node OpenCTI deployment so each node refreshes dependency status every 10 s and collects storage/ingestion metrics every 60 s.
— Exact config keys, env vars and defaults with runnable YAML examples.product docs
0200
Exponential back-off for missing-reference retriesimproved95how completely this was documenteddepth35/40specificity30/30actionability30/3095 / 100
Adds OPENCTI_MISSING_REF_RETRY_EXPONENTIAL to switch missing-reference retries from a flat random 1-3s delay to an exponential back-off schedule (averages 0.5s, 1s, 2s, 4s with jitter) applied to workers and connectors via the pycti library, OPENCTI_MISSING_REF_RETRY_INITIAL_DELAY to set the average wait before the first retry (minimum 0), and OPENCTI_MISSING_REF_RETRY_FACTOR to set the back-off multiplier applied at each retry (minimum 1; 1 = constant wait).
Enable exponential back-off for missing-reference retries in a connector environment where referenced entities often arrive within a second, reducing unnecessary wait time on early retries.
— Full env-var set with defaults and a runnable configuration example.product docs
0300
New health and usage Prometheus metricsnew80how completely this was documenteddepth30/40specificity30/30actionability20/3080 / 100
Adds opencti_dependency_up reporting connectivity state (up/down) for each dependency (elasticsearch, storage, rabbitmq, redis) as a Boolean, opencti_elasticsearch_used_size_bytes reporting total ElasticSearch/OpenSearch primary store size in bytes (replicas excluded), opencti_storage_used_size_bytes reporting total S3/MinIO bucket size in bytes, and opencti_queue_consumers reporting active consumers on push queues broken down by connector type (EXTERNAL_IMPORT, INTERNAL_ENRICHMENT, INTERNAL_IMPORT_FILE, INTERNAL_EXPORT_FILE, or UNKNOWN).
— Metrics named precisely but no scrape or query example given.product docs
0400
Redis TLS SNI server name confignew70how completely this was documenteddepth20/40specificity25/30actionability25/3070 / 100
Adds redis:tls_servername (REDIS__TLS_SERVERNAME) config key to supply an optional shared server name for TLS SNISNIA TLS extension that lets a client declare which hostname it is connecting to during the handshake, allowing one server to host multiple certificates on a single IP address. and certificate validation when running Redis in cluster mode.
Add a Redis TLS server name for SNI validation when all cluster nodes share the same certificate CN, without per-node overrides.
yaml
redis:
  tls_servername: redis.internal.example.com
— Named config key with a runnable example but thin mechanism detail.product docs
thinner coverage below
0500
User merge reattributes relations and historyimproved45how completely this was documenteddepth20/40specificity15/30actionability10/3045 / 100
Extends user merge to re-point assignee and participant relations to the target user, and to rewrite history and activity attribution to the target user.
— Describes the behaviour change but no command or UI path given.7.260921.0
0600
News Feed support for OCTI integrationsnew40how completely this was documenteddepth15/40specificity15/30actionability10/3040 / 100
Adds News Feed support for OCTI integrations (excluding connectors), surfacing a new integration resource type in the feed.
— Names the new resource type but gives no further mechanism.7.260921.0
0700
Column selection in Fintel reportsnew35how completely this was documenteddepth15/40specificity10/30actionability10/3035 / 100
Adds column selection for entity attributes in Fintel reports, letting analysts customize which fields appear in generated tables.
— Describes the capability but no UI path or config named.7.260921.0
OpenCTI 7.260921.0 adds News Feed integration support, Fintel column selection, and user-merge history reattribution.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ GET THIS VERSION
$ git clone --branch 7.260921.0 https://github.com/OpenCTI-Platform/opencti.git
# already have the repo? check out this version:$ git checkout 7.260921.0
Adds column selection for entity attributes in Fintel reports, letting analysts customize which fields appear in generated tables.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds News Feed support for OCTI integrations (excluding connectors), surfacing a new integration resource type in the feed.
Extends user merge to re-point assignee and participant relations to the target user.
Extends user merge to rewrite history and activity attribution to the target user.
Adds column selection for entity attributes in Fintel reports, letting analysts customize which fields appear in generated tables.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Tenzir is a data pipeline engine for security teams that collects, transforms, enriches, and routes telemetry.
Tenzir shipped a large batch of platform and node configuration surfaces this window — agent skills for AI coding tools spanning TQL and eight security schemas, four new TQL chart operators with dashboard export, an AWS CloudFormationAWS CloudFormationAn AWS service for declaring cloud infrastructure as code in JSON or YAML templates, letting cyber tools provision and tear down entire environments reproducibly without manual console steps. deployment path for the Platform Sovereign Edition, centralized TLS/proxy/config-file controls, and pipeline parallelismpipeline parallelismPutting successive layers of a model on different GPUs, which pass their outputs to the next stage. Different batches can move through the stages at the same time. and storage tuning knobs — alongside a v6.18.0 node release adding a recursive search function and removing the legacy non-neo executor.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
15 FEATURES1 OF 15 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Agent skills for AI coding agentsnew98how completely this was documenteddepth38/40specificity30/30actionability30/3098 / 100
Adds npx skills add tenzir/skills (also via uvx skeel add or gh skill install) to install Tenzir agent skills into Claude Code, Cursor, Codex, GitHub Copilot, and 40+ other coding agents from the tenzir/skills repository.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ The tenzir skill packages the full documentation (TQL, operators, functions, integrations, deployment, configuration) with progressive disclosure; tenzir-ocsf covers OCSFOCSFAn open schema standard, maintained by the OCSF community under CISA and industry backing, that defines a common event format so cyber tools can share and ingest log data without per-source normalization work. event classes, objects, attributes, profiles, and extensions; tenzir-ecs covers ECSECSElastic Common Schema, an open specification maintained by Elastic that defines a standard field naming convention for log and event data, letting cyber tools share and correlate records without per-source field mapping. fields, fieldsets, categorization values, custom fields, and OpenTelemetryOpenTelemetryAn open standard and set of tools for collecting traces, metrics and logs from applications. It lets services export observability data without tying instrumentation to one monitoring vendor. alignment; tenzir-cef covers the ArcSight CEFCEFCommon Event Format, an ArcSight (Micro Focus) log standard that defines a fixed header plus extensible key-value pairs so cyber tools can emit and ingest alerts in a predictable, parseable structure. standard including 174 predefined extension keys and 479 ESM data fields across 18 schema groups; tenzir-leef covers IBM QRadar LEEF 1.0/2.0 including 45 predefined event attributes and devTime/devTimeFormat patterns; tenzir-cim covers Splunk CIM 8.5 data models, datasets, fields, tags, constraints, and lookups; tenzir-asim covers Microsoft Sentinel ASIM schemas, fields, aliases, and roles; tenzir-udm covers Google SecOpsSecOpsThe practice of merging security and IT operations teams so that threat detection, response, and infrastructure management share the same workflows, giving cyber tools a single pipeline from alert to remediation. UDM ingestion payloads (e.g. metadata.eventType) and YARA-L/Detect Engine logic (e.g. $event.metadata.event_type); and tenzir-edm covers the FortiSIEM 7.5.0 Event Data Model. Skills install to project scope by default (./<agent>/skills/) or globally with -g (~/<agent>/skills/), can target specific agents with -a (e.g. -a claude-code -a cursor -a codex), and are managed via npx skills list, npx skills check, npx skills update, and npx skills remove.
Install the OCSF schema skill globally so any project's coding agent can map raw events to OCSF event classes without re-installing per repo.
$ npx skills add -g tenzir/skills@tenzir-ocsf
Install the full Tenzir docs skill scoped to Claude Code and Cursor only, then keep it current — useful in a team repo where only those two agents are standardized.
$ npx skills add tenzir/skills@tenzir -a claude-code -a cursor
npx skills update
Audit which skills are installed globally and check whether any are out of date before updating a shared developer environment.
— Every skill, flag, and subcommand named with runnable commandsproduct docs
0200
Chart operators for pipelines and dashboardsnew96how completely this was documenteddepth38/40specificity30/30actionability28/3096 / 100
Adds four TQL chart operators: chart_pie (label/x, value/y), chart_bar (x, y, group, position e.g. 'stacked', y_log), chart_line (x, y, group, resolution, x_min, x_max, y_min, y_max, fill), and chart_area (same parameters as chart_line plus position='stacked'). All support inline aggregation expressions (e.g. y=mean(current_memory_usage)), removing the need for a preceding summarize; resolution buckets time series with floor/ceiling alignment and implicit time-range filtering when combined with x_min/x_max; fill replaces empty buckets (e.g. fill=0); and group splits data into series by field value without enumerating series names. Charts can be downloaded from the Explorer or a dashboard as PNG or SVG, and added to a dashboard via the Dashboard button in the Explorer for persistent, auto-refreshing visualization.
Visualize top application types from Zeek connection logs as a pie chart — useful for a quick protocol breakdown in the Explorer.
$ export
where @name == "zeek.conn"
where service != null
top service
head
chart_pie label=service value=count
Plot per-pipeline event throughput as a multi-series line chart over the last 24 hours, bucketed into 30-minute intervals — replaces a manual where + summarize chain.
— Every operator and parameter named with runnable pipeline examplesproduct docs
0300
AWS CloudFormation deployment for Sovereign Editionnew95how completely this was documenteddepth35/40specificity30/30actionability30/3095 / 100
Deploys the Tenzir Platform Sovereign Edition on AWS via a publicly hosted CloudFormationCloudFormationAn AWS service that lets you describe and provision cloud infrastructure as declarative YAML or JSON templates, so a cyber tool can reproducibly spin up or tear down its entire AWS environment with a single API call. template (https://tenzir-marketplace-resources.s3.eu-west-1.amazonaws.com/tenzir-platform.yml) that provisions VPCVPCA logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware., ECS Fargate, Lambda, App Runner, RDS PostgreSQL, S3, Cognito, ACM, and Route53. External OIDCOIDCOpenID Connect, a sign-in protocol built on OAuth 2.0. An application uses identity information from a trusted provider instead of maintaining a separate password for each user. providers can replace Cognito via the UseExternalOIDC, ExternalOIDCIssuerURL, ExternalOIDCClientID, and ExternalOIDCClientSecret parameters, and RandomSubdomain auto-prefixes subdomains (e.g. ui.abc123.example.org) for staging or multi-tenant setups. A copy-images.sh script pulls the three Marketplace images (tenzir/se-platform-ui, tenzir/se-platform-api, tenzir/se-platform-gateway) from the AWS Marketplace ECRECRAmazon Elastic Container Registry, AWS's managed service for storing and distributing Docker and OCI container images, giving cyber tools a private, IAM-gated registry without self-hosting infrastructure. registry (709825985650.dkr.ecr.us-east-1.amazonaws.com) into a local ECR account before stack creation.
Deploy the full Tenzir Platform stack on AWS in one command, pinning to a specific image version and using your own domain.
— Runnable CloudFormation commands with exact parametersproduct docs
0400
CLI file loading and Pipelines-as-Codenew95how completely this was documenteddepth35/40specificity30/30actionability30/3095 / 100
Adds -f to the tenzir binary to load a pipeline definition from a file instead of inline. Supports Pipelines-as-CodePipelines-as-CodeA practice where CI/CD pipeline definitions are stored as version-controlled code files alongside the project they build, letting cyber tools automate, audit, and reproduce build or scan workflows consistently. by declaring pipelines under tenzir.pipelines in <prefix>/etc/tenzir/tenzir.yaml, with per-pipeline name, description, definition, restart-on-error (true/false/null or a duration like 1 minute), unstoppable (run continuously, entering a failed state if it completes), disabled (keep the definition but don't start it), and labels (tags shown on the pipeline overview page at app.tenzir.com). Also supports running open, transformation-only pipelines from the CLI that auto-complete with stdin/stdout, with output format selectable via operators such as write_csv, write_ssv, and write_parquet.
Run a saved pipeline file instead of inlining the definition — useful for complex or version-controlled pipelines in CI.
$ tenzir -f pipeline.tql
Deploy a persistent Suricata ingest pipeline as code so it starts automatically with the node and restarts on failure.
yaml
tenzir:
  pipelines:
    suricata-over-tcp:
      name: Onboard Suricata from TCP
      description: |
        Onboards Suricata EVE JSON from TCP port 34343.
      definition: |
        accept_tcp "0.0.0.0:34343" {
          read_suricata
        }
        publish "suricata"
      restart-on-error: 1 minute
      labels:
        - Suricata
        - Onboarding
      disabled: false
      unstoppable: true
Parse a YAML file from stdin, filter a field, and write the result as CSV to stdout — no source or sink operators needed.
— All config fields and CLI flags named with runnable examplesproduct docs
0500
Centralized TLS configuration in tenzir.yamlnew94how completely this was documenteddepth36/40specificity30/30actionability28/3094 / 100
Adds a tenzir.tls block in tenzir.yaml with enable, skip-peer-verification, cacert, certfile, keyfile, password, tls-min-version, and tls-ciphers to configure TLS once for all compatible operators (accept_relp, accept_splunk, from_http, to_opensearch, accept_opensearch, to_splunk). tls-client-ca and require-client-cert under tenzir.tls enable mutual TLSmutual TLSMutual TLS, an encrypted connection where both client and server present certificates to prove their identity. It helps services verify who they are communicating with., rejecting clients without a certificate signed by the configured CA. A separate plugins.platform TLS block (skip-peer-verification, cacert, certfile, keyfile, tls-min-version, tls-ciphers) configures outbound TLS exclusively for the node-to-platform connection, overriding node-level settings. Documentation also names the node-level keys tenzir.tls.min-version ("1.0"–"1.3") and tenzir.tls.ciphers (an OpenSSL cipher list) explicitly, covering to_opensearch, to_splunk, accept_tcp, from_tcp, serve_tcp, and accept_opensearch, and clarify that tls-min-version/tls-ciphers in <configdir>/tenzir/plugin/platform.yaml take precedence for Platform connections.
Enforce a minimum TLS 1.2 and a restricted cipher suite across all Tenzir operators in one place, rather than repeating TLS flags on every pipeline operator.
Require clients to authenticate with a certificate when connecting to server-mode operators, enabling mutual TLS so unauthenticated clients are rejected.
Enforce TLS 1.2 minimum and restrict cipher suites for all node outbound and inbound connections (e.g. to Splunk, OpenSearchOpenSearchAn open-source search and analytics engine, forked from Elasticsearch by AWS in 2021, that lets cyber tools store, query, and visualize large volumes of log or event data without licensing restrictions., or TCPTCPA network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. listeners).
— Full set of TLS keys and precedence rules named with examplesproduct docs
0600
Internal services config for Tenzir Platformnew90how completely this was documenteddepth32/40specificity30/30actionability28/3090 / 100
Adds environment variables for the Tenzir Platform's internal services: TENZIR_PLATFORM_ADMIN_RULES defines which users get admin access using rules like auth_allow_all or auth_user with a user_id (generate rules with tenzir-platform tools print-auth-rule); TENZIR_PLATFORM_INTERNAL_AUTH_SECRET, TENZIR_PLATFORM_INTERNAL_TENANT_TOKEN_ENCRYPTION_KEY, and TENZIR_PLATFORM_INTERNAL_APP_API_KEY set per-instance encryption and API secrets; BLOB_STORAGE__NODES_PUBLIC_ENDPOINT_URL lets nodes on separate networks reach S3-compatibleS3-compatibleAn object-storage API that mirrors Amazon S3's HTTP interface, so any client or cyber tool written for AWS S3 works unchanged against any compliant storage backend. blob storage via a different URL than the UI uses; TENZIR_PLATFORM_USE_INTERNAL_WS_PROXY routes UI frontend requests through the UI backend instead of directly to the Tenzir Gateway for zero-trust topologies; PRIVATE_JWT_FROM_HEADER accepts externally-supplied JWTsJWTsJSON Web Tokens — an open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object. Cyber tools use them for stateless authentication without server-side session storage. from an HTTP header (e.g. X-Goog-IAP-JWT-Assertion) for proxies like Google Cloud IAP; and CORS_ALLOWED_ORIGINS on the websocket-gateway service in docker-compose.yaml allows UI origins when the gateway and UI are on different domains.
Restrict platform admin rights to two specific Google OAuth2OAuth2An open authorization framework (RFC 6749) that lets a service grant limited access to a user's resources on another service without exposing credentials, giving cyber tools a standard way to authenticate against third-party APIs. users in a production deployment.
Accept Google Cloud IAP JWTs from the standard assertion header so users behind IAP skip the OIDC login flow.
env
PRIVATE_JWT_FROM_HEADER=X-Goog-IAP-JWT-Assertion
— Every env var named with example values, no limits givenproduct docs
0700
Storage, batching, and catalog tuning config keysnew90how completely this was documenteddepth34/40specificity30/30actionability26/3090 / 100
Adds a set of tenzir.yaml keys to tune node performance: tenzir.demand.max-batches caps in-memory topic buffering for publish/subscribe; tenzir.import.batch-size (default 8,192) bounds events per table slice; tenzir.import.batch-timeout forwards buffered slices before they reach batch-size; tenzir.import.read-timeout (default 10 seconds) controls how long a read blocks before retrying; tenzir.max-partition-size (default 4Mi / 2^22 records) bounds partition size and catalog memory footprint; tenzir.active-partition-timeout (default 10 seconds) closes active partitions by time rather than record count; tenzir.index.rules defines per-field/per-type catalog sketch rules with targets and fp-rate, with tenzir.index.default-fp-rate setting the type-level default; and tenzir.zstd-compression-level tunes Zstd compression for partitions at rest.
Reduce catalog false-positive rate for a high-cardinality URL field and all IP fields to cut down irrelevant partition reads.
— Every config key and default named with one worked exampleproduct docs
0800
Node proxy, subprocess, and endpoint controlsnew88how completely this was documenteddepth32/40specificity28/30actionability28/3088 / 100
Adds tenzir.pipeline-subprocesses: true (or TENZIR_PIPELINE_SUBPROCESSES=true) in tenzir.yaml to run pipeline execution in subprocesses for improved error resilience and resource utilization. Adds tenzir.http-proxy, tenzir.https-proxy, and tenzir.no-proxy to route outbound operator traffic through an HTTP proxy with per-host/CIDRCIDRA notation for a block of IP addresses, such as 10.0.0.0/24. The number after the slash says how many leading address bits identify the network. bypass. tenzir.endpoint can be set to false to disable node-to-node TCP connections (making the node reachable only via the Tenzir Platform) or to a custom address to override the default 127.0.0.1:5158 listener, including IPv6IPv6The current version of the Internet Protocol, standardized by the IETF, using 128-bit addresses to replace the exhausted IPv4 space. Cyber tools target it because modern networks run dual-stack or IPv6-only..
Route all outbound operator traffic through a corporate proxy while bypassing it for internal RFC-1918 ranges.
Enable pipeline subprocesses to isolate faults and improve resource utilisation without changing the binary invocation.
yaml
tenzir:
  pipeline-subprocesses: true
Harden a cloud-only node by disabling direct TCP access so only the Tenzir Platform can reach it.
yaml
tenzir:
  endpoint: false
Route all Tenzir outbound HTTPSHTTPSHTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate. and gRPCgRPCAn open-source remote procedure call framework from Google that uses HTTP/2 and Protocol Buffers to let services call each other's functions across a network, giving tools low-latency, strongly typed inter-process communication. traffic through a corporate proxy, bypassing it for internal subnets.
— All config keys named with runnable YAML snippetsproduct docs
0900
Pipeline parallelism controlsimproved85how completely this was documenteddepth35/40specificity28/30actionability22/3085 / 100
Adds a // parallelism: <n> pipeline directive (accepting disabled, max, or a positive integer) to run CPUCPUThe main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware.-bound operators across multiple cores, with a node-wide default settable via tenzir.parallelism in tenzir.yaml. fuse=none, fuse=all, and fuse=parallel options control whether operators are fused into a single group, limit_partitions=<n> caps instances for partition-keyed operators like summarize, group, and deduplicate, and a transform parallel { … } block operator (with its own fuse=<value>) parallelizes just a CPU-bound subsection of a pipeline. Parallel execution was subsequently enabled by default for asynchronous transforms (increasing throughput for DNS, context, and Python workloads) and for competing-consumer sources (increasing throughput for AMQP and Google Cloud Pub/Sub workloads).
Config file discovery and per-plugin config filesnew68how completely this was documenteddepth22/40specificity24/30actionability22/3068 / 100
Adds --bare-mode to disable all system- and user-specified configuration path lookups (for script-wrapping use cases) and --config=/path/to/tenzir.yaml to explicitly specify a config file path at startup. Also supports plugin-specific configuration files at <configdir>/tenzir/plugin/<plugin>.yaml as an alternative to inline plugins.<name> entries in tenzir.yaml.
— Flags and path named but no worked exampleproduct docs
thinner coverage below
1100
Predefined dashboards in workspace.yamlnew57how completely this was documenteddepth20/40specificity22/30actionability15/3057 / 100
Adds a dashboards key under workspaces.<id> in workspace.yaml to pre-define dashboards for static workspaces, with named cells, a pipeline definition, a visualization type (table, bar, line, etc.), and grid coordinates (x, y, w, h).
— Config key named but no worked example providedproduct docs
1201
Legacy non-neo executor removedbreaking43how completely this was documenteddepth18/40specificity15/30actionability10/3043 / 100
The legacy non-neo executor has been removed; pipelines relying on the legacy executor must migrate to the neo executor.
runZero is an asset discovery and inventory platform that identifies and maps all devices on networks without requiring agents.
runZero's biggest window additions are a vulnerability suppression/unsuppression API, an OCSF 1.9.0OCSF 1.9.0An open schema standard, maintained by the OCSF community under CISA and industry backing, that defines a common event format for security telemetry so cyber tools can share and ingest logs without custom normalization. export and a new Cryptographic Bill of MaterialsBill of MaterialsA structured list of every component, library, and dependency that makes up a piece of software or hardware, used by cyber tools to track what is inside a product and surface known vulnerabilities in its parts. (CBOMCBOMA structured inventory of cryptographic assets — algorithms, keys, certificates, and protocols — used in a system, modeled after the Software Bill of Materials concept to help teams audit and manage cryptographic risk.) export, alongside OAuth support for MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface., more granular custom roles and API-client permissions, and a round of scripting, reporting, and performance improvements.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
17 FEATURES4 OF 17 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
OCSF 1.9.0 export from asset inventorynew80how completely this was documenteddepth35/40specificity25/30actionability20/3080 / 100
Adds an OCSFOCSFAn open schema standard, maintained by the OCSF community under CISA and industry backing, that defines a common event format so cyber tools can share and ingest log data without per-source normalization work. 1.9.0 export from the asset inventory, exporting assets as Device Inventory Info events and observed services as Live Evidence Info events, available from the inventory export menu and the Export API.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Fields without an OCSF equivalent are preserved under the event's unmapped object.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Custom integration scripting enhancementsnew75how completely this was documenteddepth30/40specificity25/30actionability20/3075 / 100
Enables running custom integration scripts on console instances in addition to Explorers and the CLI. Adds an in-product script authoring and testing environment using the AI model of your choice. Scripts now support settings shared across protocols like HTTP and TLS. Allows users to submit scripts for inclusion as native runZero sources.
Custom roles and granular permissions across API keys, users, groups, and SSOnew70how completely this was documenteddepth30/40specificity25/30actionability15/3070 / 100
Supports assigning custom roles to API keys, default user roles, group permissions, SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. defaults, and MCP connections. API clients can now be created with custom permissions capped by the creating user's own access rights, and account-level API clients can use granular authentication scopes in addition to roles. The list of default roles selectable in SSO settings now includes the Annotator role.
Cryptographic Bill of Materials (CBOM) exportnew65how completely this was documenteddepth20/40specificity20/30actionability25/3065 / 100
Adds a Cryptographic Bill of Materials (CBOM) as a new CycloneDXCycloneDXAn open standard for describing software components and their dependencies, vulnerabilities and other supply-chain information. Tools use it to exchange bills of materials and related evidence. JSON export and detailed report, letting users identify weak or deprecated algorithms across the asset inventory.
Generate a Cryptographic Bill of Materials for an org to identify weak or deprecated algorithms across the asset inventory.
📍In the runZero console, go to Reports, select Cryptographic Bill of Materials (CBOM), then choose Export as CycloneDX JSON to download the artifact.
OAuth support for MCP servicenew65how completely this was documenteddepth25/40specificity25/30actionability15/3065 / 100
Adds OAuth support to the MCP service, including the ability to use Export Tokens and Organization Keys as OAuth Client Secrets, in addition to API Clients.
AI-generated content labelingnew55how completely this was documenteddepth25/40specificity20/30actionability10/3055 / 100
runZero now labels AI Threads and AI Artifacts as AI-generated, embeddingembeddingLists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. the label in exported reports, downloaded files, and generated custom-integration scripts.
Promiscuous ARP probe toggle on scan pagenew50how completely this was documenteddepth15/40specificity15/30actionability20/3050 / 100
Adds a configuration option on the scan page to toggle the promiscuous ARPARPA network protocol that maps IP addresses to MAC addresses on a local Ethernet segment, letting tools resolve layer-3 targets to layer-2 hardware addresses for packet crafting or host discovery. probe.
Reports page and External Reporting enhancementsimproved50how completely this was documenteddepth20/40specificity15/30actionability15/3050 / 100
The reports page now displays a paginated, searchable list of all analysis task-based reports with delete support. Users can now share standard reports through the External Reporting feature.
Performance improvements across scanning, tasks, and exportsimproved45how completely this was documenteddepth20/40specificity20/30actionability5/3045 / 100
runZero optimized MAC merging so large scan jobs now process faster, now processes directory and device data concurrently to improve task performance, sped up vulnerability exports, and no longer counts background MCP connections against API usage.
runZero adds vulnerability suppression API, OCSF 1.9.0OCSF 1.9.0An open schema standard, maintained by the OCSF community under CISA and industry backing, that defines a common event format for security telemetry so cyber tools can share and ingest logs without custom normalization. export, CBOMCBOMA structured inventory of cryptographic assets — algorithms, keys, certificates, and protocols — used in a system, modeled after the Software Bill of Materials concept to help teams audit and manage cryptographic risk.CycloneDXCycloneDXAn open standard for describing software components and their dependencies, vulnerabilities and other supply-chain information. Tools use it to exchange bills of materials and related evidence. JSON, OAuth for MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface., and custom API key roles.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
Generate a Cryptographic Bill of MaterialsBill of MaterialsA structured list of every component, library, and dependency that makes up a piece of software or hardware, used by cyber tools to track what is inside a product and surface known vulnerabilities in its parts. for an org to identify weak or deprecated algorithms across the asset inventory.
📍In the runZero console, go to Reports, select Cryptographic Bill of Materials (CBOM), then choose Export as CycloneDX JSON to download the artifact.
Adds vulnerability suppression and unsuppression via the runZero API, covering vulnerabilities, vulnerability groups, and findings.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds an OCSF 1.9.0 export from the asset inventory, exporting assets as Device Inventory Info events and observed services as Live Evidence Info events, available from the inventory export menu and the Export API; fields without an OCSF equivalent are preserved under the event's unmapped object.
Adds a Cryptographic Bill of Materials (CBOM) as a new CycloneDX JSON export and detailed report.
Adds OAuth support to the MCP service, including the ability to use Export Tokens and Organization Keys as OAuth Client Secrets, in addition to API Clients.
Supports assigning custom roles to API keys, default user roles, group permissions, SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. defaults, and MCP connections.
+23 moreshow less
Enables creating API clients with custom permissions capped by the creating user's own access rights; account-level API clients can now use granular authentication scopes in addition to roles.
Adds a configuration option on the scan page to toggle the promiscuous ARPARPA network protocol that maps IP addresses to MAC addresses on a local Ethernet segment, letting tools resolve layer-3 targets to layer-2 hardware addresses for packet crafting or host discovery. probe.
Adds Mermaid-based charting and diagram support to the AI Threads feature.
Enables running custom integration scripts on console instances in addition to Explorers and the CLI.
Adds an in-product script authoring and testing environment using the AI model of your choice.
Scripts now support settings shared across protocols like HTTP and TLS.
Allows users to submit scripts for inclusion as native runZero sources.
The reports page now displays a paginated, searchable list of all analysis task-based reports with delete support.
Adds a Dashboards column to the query library showing how many personal dashboards use a saved query and whether it appears on other dashboards.
The list of default roles selectable in SSO settings now includes the Annotator role.
WS-Discovery XAddr endpoints now contribute to asset hostnames.
Adds the ability to sort Findings by name.
Adds the ability to close an Issue directly from the Issue Details page.
Users can now reprocess tasks directly from the user interface.
Users can now share standard reports through the External Reporting feature.
Task summaries now indicate when a task involved more than 1,000 asset changes.
Issue owners now receive an email with a direct link when assigned an Issue.
runZero now labels AI Threads and AI Artifacts as AI-generated, embeddingembeddingLists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. the label in exported reports, downloaded files, and generated custom-integration scripts.
Users can now re-invite an external user who already has access to the account.
runZero optimized MAC merging so large scan jobs now process faster.
runZero now processes directory and device data concurrently, improving task performance.
Vulnerability exports now run faster.
Background MCP connections no longer count against API usage.
Adds vulnerability suppression and unsuppression via the runZero API, covering vulnerabilities, vulnerability groups, and findings.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds an OCSF 1.9.0 export from the asset inventory, exporting assets as Device Inventory Info events and observed services as Live Evidence Info events, available from the inventory export menu and the Export API; fields without an OCSF equivalent are preserved under the event's unmapped object.
Adds a Cryptographic Bill of Materials (CBOM) as a new CycloneDX JSON export and detailed report.
Adds OAuth support to the MCP service, including the ability to use Export Tokens and Organization Keys as OAuth Client Secrets, in addition to API Clients.
Adds a configuration option on the scan page to toggle the promiscuous ARPARPA network protocol that maps IP addresses to MAC addresses on a local Ethernet segment, letting tools resolve layer-3 targets to layer-2 hardware addresses for packet crafting or host discovery. probe.
+4 moreshow less
Adds an in-product script authoring and testing environment using the AI model of your choice.
Allows users to submit scripts for inclusion as native runZero sources.
Issue owners now receive an email with a direct link when assigned an Issue.
runZero now labels AI Threads and AI Artifacts as AI-generated, embeddingembeddingLists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. the label in exported reports, downloaded files, and generated custom-integration scripts.
Censys shipped a new ServiceNow TISC integration for enriching, rescanning, and pivoting on assets directly from ServiceNow, alongside 16 new platform fingerprints and two new ASMASMAttack Surface Management: the continuous practice of discovering, inventorying, and monitoring an organization's externally exposed assets so that cyber tools can flag unknown or misconfigured entry points before attackers find them. risk fingerprints for exposed management interfaces and a Cisco vulnerability.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Censys is a search engine for internet-connected devices that indexes servers, certificates, and host data for security research and threat intelligence.
Censys shipped a new ServiceNow TISC integration for enriching, rescanning, and pivoting on assets directly from ServiceNow, alongside 16 new platform fingerprints and two new ASMASMAttack Surface Management: the continuous practice of discovering, inventorying, and monitoring an organization's externally exposed assets so that cyber tools can flag unknown or misconfigured entry points before attackers find them. risk fingerprints for exposed management interfaces and a Cisco vulnerability.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
3 FEATURES2 OF 3 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0101
New ASM risk fingerprints for exposed and vulnerable assetsnew88how completely this was documenteddepth30/40specificity30/30actionability28/3088 / 100
Adds two new ASM risk fingerprints, queryable via the risks.name field: "Exposed Check Point Security Management and Log Server" to find internet-exposed management-plane assets, and "Vulnerable Cisco Secure Email Gateway [CVE-2026-76461]" to identify assets affected by the actively-exploited SQL injectionSQL injectionAn attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does. vulnerability CVE-2026-76461.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Find all internet-exposed Check Point Security Management or Log Servers in your ASM workspace to prioritize remediation of management-plane exposure.
$ risks.name: "Exposed Check Point Security Management and Log Server"
Identify assets running a version of Cisco Secure Email Gateway affected by the actively-exploited SQL injection vulnerability CVE-2026-76461.
ServiceNow TISC integrationnew64how completely this was documenteddepth28/40specificity22/30actionability14/3064 / 100
Adds a ServiceNow TISC integration that can automatically or manually enrich IPs, web properties, and certificates in ServiceNow TISC with Censys Platform data. From within ServiceNow TISC, users can also initiate a Censys rescan of a host or web property, retrieve scan history for an IP address, and initiate a CensEye automated pivoting job to find assets related to an IP, web property, or certificate.
16 new platform fingerprintsnew53how completely this was documenteddepth15/40specificity30/30actionability8/3053 / 100
Adds 16 new platform fingerprints covering Check Point Security Management and Log Server, Apache CloudStack, Apache Cocoon, Cisco Secure Email Gateway, Citrix XenMobile Server, Docker Registry Browser, GeoVision GeoWebServer, IBM WebSphere Liberty, Lucee, OpenMetadata, phpList, Plone, PrivateBin, pypiserver, Roadiz CMSCMSA web content management system for creating and managing digital content without writing code directly; cyber tools use CMS platforms to host documentation, portals, or reporting dashboards quickly., and TYPO3.
Censys adds ServiceNow TISC integration, 16 new platform fingerprints, and two new ASMASMAttack Surface Management: the continuous practice of discovering, inventorying, and monitoring an organization's externally exposed assets so that cyber tools can flag unknown or misconfigured entry points before attackers find them. risk fingerprints.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Find all internet-exposed Check Point Security Management or Log Servers in your ASM workspace to prioritize remediation of management-plane exposure.
$ risks.name: "Exposed Check Point Security Management and Log Server"
Identify assets running a version of Cisco Secure Email Gateway affected by the actively-exploited SQL injectionSQL injectionAn attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does. vulnerability CVE-2026-76461.
Adds a ServiceNow TISC integration to automatically or manually enrich IPs, web properties, and certificates in ServiceNow TISC with Censys Platform data.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds the ability to initiate a Censys rescan of a host or web property directly from ServiceNow TISC.
Adds the ability to retrieve scan history for an IP address from within ServiceNow TISC.
Adds the ability to initiate a CensEye automated pivoting job from ServiceNow TISC to find assets related to an IP, web property, or certificate.
Adds 16 new platform fingerprints covering Check Point Security Management and Log Server, Apache CloudStack, Apache Cocoon, Cisco Secure Email Gateway, Citrix XenMobile Server, Docker Registry Browser, GeoVision GeoWebServer, IBM WebSphere Liberty, Lucee, OpenMetadata, phpList, Plone, PrivateBin, pypiserver, Roadiz CMSCMSA web content management system for creating and managing digital content without writing code directly; cyber tools use CMS platforms to host documentation, portals, or reporting dashboards quickly., and TYPO3.
Adds a ServiceNow TISC integration to automatically or manually enrich IPs, web properties, and certificates in ServiceNow TISC with Censys Platform data.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds the ability to initiate a Censys rescan of a host or web property directly from ServiceNow TISC.
Adds the ability to retrieve scan history for an IP address from within ServiceNow TISC.
Adds the ability to initiate a CensEye automated pivoting job from ServiceNow TISC to find assets related to an IP, web property, or certificate.
DefectDojo's main addition this window is an asset hierarchy feature that suggests deploys to relationships from container image evidence, backed by scanners now emitting image locations into the Locations model; a smaller performance fix debounces product grade recalculation.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
3 FEATURES0 OF 3 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Suggested deploy-to edges from container evidencenew79how completely this was documenteddepth35/40specificity26/30actionability18/3079 / 100
When Container Image Locations are enabled, DefectDojo detects undrawn deploys to relationships by matching image repositories across assets and surfaces each pair as a reviewable suggestion on the asset hierarchy page, backed by container-image evidence.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Accepting a suggestion draws the deploys to edge from the image-building asset to the running asset (the deployed asset inherits its host's exposure) and the accepted edge carries an origin of container evidence to distinguish it from manually drawn or connector-declared edges; dismissing a suggestion suppresses that asset pair (further images for the pair are counted but do not reopen it, and dismissed suggestions can be reopened from the same dialog). Reviewing suggestions requires the Asset Hierarchy view permission, while accepting or dismissing requires the edit permission plus edit access to both assets.
Review and accept container-derived deploy relationships on the asset hierarchy page to propagate exposure from host assets to deployed assets automatically.
📍In the Asset Hierarchy page, look for the banner counting open suggestions, click Review to open the list, then click Accept on a pair to draw the deploys-to edge, or Dismiss to suppress it.
— Full mechanism, permissions, and UI path given; no exact endpoint/flag.product docs
thinner coverage below
0200
Container image location emission from scannersnew46how completely this was documenteddepth20/40specificity18/30actionability8/3046 / 100
Container scanners now emit the scanned image as an Image location, linking container images to their repository in the Locations model. This is the underlying data source that powers the asset hierarchy's deploy-to suggestions.
— Names the `Image` location and Locations model but no usage steps.3.3.200
0300
Debounced product grade recalculationimproved24how completely this was documenteddepth12/40specificity8/30actionability4/3024 / 100
Product grade recalculation is now debounced per product to improve performance on large imports.
— One-line performance note with no mechanism or numbers.3.3.200
DefectDojo 3.3.200 adds container image location emission from container scanners and debounced product grade recalculation.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ GET THIS VERSION
$ git clone --branch 3.3.200 https://github.com/DefectDojo/django-DefectDojo.git
# already have the repo? check out this version:$ git checkout 3.3.200
Container scanners now emit the scanned image as an Image location, linking container images to their repository in the Locations model.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Debounces product grade recalculation per product to improve performance on large imports.
Container scanners now emit the scanned image as an Image location, linking container images to their repository in the Locations model.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Okta introduced a full AI Agent identity platform — Agent Gateway runtime enforcement, Agent SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management., shadow AI discovery, ephemeral credentialing, HITLHITLHuman in the loop, involving a person in an otherwise automated workflow. The person can review, approve, correct or supply information before work continues. guardrails, ISPMISPMIdentity Security Posture Management: a discipline for continuously discovering, assessing, and remediating identity-related risks across users, accounts, and entitlements, giving cyber tools a unified view of identity exposure., and FedRAMPFedRAMPA US government program that standardizes cloud security authorization, letting vendors get a single assessment accepted across federal agencies instead of repeating the process for each one./DoD/HIPAAHIPAAA US federal law enacted in 1996 that sets privacy and security requirements for protected health information, giving cyber tools a compliance baseline to enforce or audit against. compliance tiers — alongside the 2026.09.0 platform release adding MCP server DCR/OIN registration, new malware-proxy and remote-desktop network zone categories, NFC and Linux authenticators, and a wide set of admin console, provisioning, and limit improvements.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Okta introduced a full AI Agent identity platform — Agent Gateway runtime enforcement, Agent SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management., shadow AI discovery, ephemeral credentialing, HITLHITLHuman in the loop, involving a person in an otherwise automated workflow. The person can review, approve, correct or supply information before work continues. guardrails, ISPMISPMIdentity Security Posture Management: a discipline for continuously discovering, assessing, and remediating identity-related risks across users, accounts, and entitlements, giving cyber tools a unified view of identity exposure., and FedRAMPFedRAMPA US government program that standardizes cloud security authorization, letting vendors get a single assessment accepted across federal agencies instead of repeating the process for each one./DoD/HIPAAHIPAAA US federal law enacted in 1996 that sets privacy and security requirements for protected health information, giving cyber tools a compliance baseline to enforce or audit against. compliance tiers — alongside the 2026.09.0 platform release adding MCP server DCR/OIN registration, new malware-proxy and remote-desktop network zone categories, NFC and Linux authenticators, and a wide set of admin console, provisioning, and limit improvements.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
29 FEATURES18 OF 29 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0101
New IP service categories in Enhanced Dynamic Network Zonesnew95how completely this was documenteddepth35/40specificity30/30actionability30/3095 / 100
Adds REMOTE_DESKTOP IP service category to Enhanced Dynamic Network Zones, letting admins include or exclude remote-desktop traffic in global session and app sign-in policies for precise access control.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds MALWARE_PROXIES IP service category, powered by Okta CyberDefense, covering proxy services tied to malware and botnet activity including 911 S5, NSOCKS, iProxy, and BHProxies.
Block access from known malware proxy networks by adding the MALWARE_PROXIES category to an Enhanced Dynamic Network Zone and denying it in the global session policy.
📍In the Admin Console, go to Security › Networks, open or create an Enhanced Dynamic Network Zone, add MALWARE_PROXIES to the excluded IP service categories, then go to Security › Global Session Policy and add a rule that denies access when the network zone matches.
Block remote-desktop originating traffic at the app sign-in policy level using the new REMOTE_DESKTOP IP service category.
📍In the Admin Console, go to Security › Networks, open or create an Enhanced Dynamic Network Zone, add REMOTE_DESKTOP to the excluded IP service categories, then open the target app's Sign-on Policy and add a rule denying access when the zone matches.
MCP server registration via OIN catalog and DCRnew80how completely this was documenteddepth30/40specificity25/30actionability25/3080 / 100
Supports Dynamic Client Registration (DCR) when manually registering an MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. server so Okta automatically registers a client with the provider and populates credentials. MCP servers can also be added directly from an Okta Integration Network (OINOINOpen Invention Network, a non-profit patent consortium that acquires patents and licenses them royalty-free to members, shielding Linux and related open-source software from patent litigation.) catalog entry, eliminating manual connection-detail entry, and tool discovery at registration time lets admins test credentials and view available tools before completing setup. The MCP server registration UI was updated with improved scope handling and tool visibility.
Register an MCP server from the OIN catalog to avoid manually entering connection details and immediately discover its available tools.
📍In the Admin Console, go to Applications › MCP Servers, click Add MCP Server, select Add from OIN catalog, locate the provider entry, choose Dynamic Client Registration (DCR) as the registration method, and click Test credentials and discover tools to verify the connection.
Failed WebAuthn enrollment logging in System Lognew80how completely this was documenteddepth30/40specificity30/30actionability20/3080 / 100
Logs failed WebAuthnWebAuthnA web standard that lets a browser prove possession of a passkey or hardware key to a website. It is the browser-facing part of FIDO2 sign-in. (FIDO2FIDO2The open standard behind passkeys and hardware security keys, where a website checks a signature from the user's device instead of a password. Because the key is bound to the site, phishing pages cannot use it.) enrollment attempts in the System Log under the user.mfa.factor.activate event, with debug data including AAGUIDAAGUIDA 128-bit identifier embedded in a FIDO2/WebAuthn authenticator that identifies the make and model of the device, letting relying parties enforce authenticator policy without tracking individual users., isBackupEligible, and matched authenticator groups.
Okta Integration Wizard for custom app integrationsnew70how completely this was documenteddepth30/40specificity25/30actionability15/3070 / 100
Introduces the Okta Integration Wizard (OIW) to create and deploy custom app integrations configuring SSO, SCIMSCIMA standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave. provisioning, Entitlement Management, Universal Logout, API service integration, and custom API Integration Actions — reusable as a template across multiple app instances.
FedRAMP, DoD IL5, and HIPAA compliance tiersnew65how completely this was documenteddepth30/40specificity25/30actionability10/3065 / 100
The Okta for AI Agents Core SKU supports FedRAMP ModerateFedRAMP ModerateA US government authorization tier requiring cloud services to meet a defined set of NIST 800-53 controls before federal agencies can use them, giving cyber tools a pre-vetted compliance baseline for government contracts./High and DoD Impact Level 5 environments, covering agent registration, cryptographic authentication, lifecycle provisioning, and SIEMSIEMSecurity information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents.-integrated audit logging. The full Okta for AI Agents SKU adds HIPAA support, including ISPM and Okta Privileged Access (OPAOPAOpen Policy Agent, a CNCF-graduated policy engine that evaluates rules written in the Rego language against JSON-structured data, letting tools enforce authorization and compliance decisions without hardcoding logic.) capabilities.
— Names SKUs and compliance scopes, no purchase/config stepsproduct docs
0605
NFC authenticator for frontline workersnew65how completely this was documenteddepth30/40specificity20/30actionability15/3065 / 100
Adds NFCNFCNear Field Communication, a short-range (≤4 cm) wireless standard maintained by the NFC Forum, enabling data exchange between devices; cyber tools use it to probe, emulate, or intercept contactless card and tag transactions. authenticator support for frontline workers on Windows shared workstations — users tap an NFC badge and enter a PIN to meet MFAMFAMulti-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. requirements without a phone, password, or shared account.
Unified identity management for AI agentsnew65how completely this was documenteddepth30/40specificity20/30actionability15/3065 / 100
Admins can set an external identifier to enforce uniqueness, configure creation and matching criteria for imported AI agents, and preview imports before registration. The AI agent Client Registration tab now displays authentication methods vertically with a Configure button linking to per-method configuration pages.
Low-Code Sign In Customizationnew65how completely this was documenteddepth30/40specificity20/30actionability15/3065 / 100
Lets admins modify text, colors, and images in the Sign-In Widget and Interstitial authentication using a JSON templating language with syntax highlighting and suggestions — no code editor required.
Entitlement import safeguards for app provisioningnew65how completely this was documenteddepth30/40specificity20/30actionability15/3065 / 100
Adds entitlement import safeguards configurable per app using percentage-based or absolute count thresholds to prevent accidental removal of app roles or licenses on user unassignment, with an option to block imports that modify or delete entitlement schemas.
Higher Access Request configuration limitsimproved65how completely this was documenteddepth25/40specificity30/30actionability10/3065 / 100
Increases Access Request limits: users per task or question to 25 (from 10), entitlement bundles in an access level condition to 1,000 (from 100), groups in an access level condition to 1,000 (from 500), request type configuration lists per org to 250 (from 100), and request types per org to 750 (from 500).
Shadow AI discovery and Universal Directory registrationnew60how completely this was documenteddepth30/40specificity20/30actionability10/3060 / 100
Multi-surface shadow AI discovery continuously scans browsers, managed endpoints, and cloud environments to uncover unvetted agents and unauthorized OAuth consent grants; discovered agents are then registered into Universal Directory alongside workforce users, with explicit human ownership, business purpose, and cryptographic credentials assigned.
— Explains scanning surfaces and registration fields, no UI stepsproduct docs
1200
Prompt-level MCP tool scopingnew60how completely this was documenteddepth30/40specificity20/30actionability10/3060 / 100
Filters unauthorized MCP tools based on the delegating user's identity before the model executes, reducing schema token overhead by over 90%.
— Has concrete metric but no setup stepsproduct docs
1310
Okta Verify for Linux desktopnew60how completely this was documenteddepth25/40specificity25/30actionability10/3060 / 100
Extends Okta Verify with official Linux desktop support (Ubuntu 24.04 and 26.04), enabling phishing-resistant, hardware-backed Okta FastPass for Linux users.
HA and incremental imports for Generic Database connectorimproved60how completely this was documenteddepth30/40specificity20/30actionability10/3060 / 100
Supports high availability for the On-prem Connector for Generic Databases by allowing multiple Okta On-Premises SCIM Agents to be assigned to a single app instance, and adds incremental imports that retrieve only users and entitlement assignments changed since the last successful import.
Applications page filtering, search, and exportimproved60how completely this was documenteddepth25/40specificity20/30actionability15/3060 / 100
Enhances the Applications page with filtering by type and status, search by name or client ID, a last-modified-date view, and CSV export for audit-ready reports.
Okta On-prem SCIM agent replaces SCIM Server agentbreaking60how completely this was documenteddepth25/40specificity20/30actionability15/3060 / 100
Replaces Okta On-prem SCIM Server agent with Okta On-prem SCIM agent, reducing dependencies and enabling new features; existing deployments referencing the old agent name must migrate to the new Okta On-prem SCIM agent.
Agent Gateway for AI agent identity verificationnew55how completely this was documenteddepth30/40specificity15/30actionability10/3055 / 100
Agent Gateway verifies agent identity, brokers credentials at runtime, and logs every tool call, all without requiring code changes to agents or tools.
— Describes mechanism but no config surface or UI pathproduct docs
1813
Ephemeral secretless credentialing for agentsnew50how completely this was documenteddepth25/40specificity15/30actionability10/3050 / 100
Issues ephemeral, secretless tokens and dynamically vaults credentials to eliminate static API keys and standing administrative access for AI agents.
— Clear mechanism, no config keys or commands givenproduct docs
1900
Human-in-the-loop guardrails for high-risk actionsnew50how completely this was documenteddepth25/40specificity15/30actionability10/3050 / 100
Requires step-up human approval before high-risk agent actions such as financial transactions, bulk database exports, or permission changes.
— Names risk categories, no configuration pathproduct docs
2014
AD/LDAP agent disruption and recovery email notificationsnew50how completely this was documenteddepth20/40specificity15/30actionability15/3050 / 100
Adds email notifications for Active DirectoryActive DirectoryMicrosoft's directory service for Windows networks that centralises authentication and authorisation; cyber tools target or integrate with it because it controls identity and access across most enterprise environments. and LDAPLDAPA protocol for querying and modifying directory services, standardized under RFC 4511, commonly used to look up users, groups, and attributes in corporate identity stores like Active Directory. agent disruption and recovery, configurable in the Admin Console.
New provisioning integrations: WordPress, Ivanti, Chef, Vercel, Sophosnew50how completely this was documenteddepth15/40specificity25/30actionability10/3050 / 100
Adds provisioning support for WordPress, Ivanti, Progress Chef, Vercel, and Sophos Cloud integrations.
Okta On-prem SCIM Server agent has been replaced by Okta On-prem SCIM agent — existing deployments referencing the old agent name must migrate to the new Okta On-prem SCIM agent.
Okta 2026.09.0 adds AI agent identity management, MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. server DCR and OINOINOpen Invention Network, a non-profit patent consortium that acquires patents and licenses them royalty-free to members, shielding Linux and related open-source software from patent litigation. catalog support, NFCNFCNear Field Communication, a short-range (≤4 cm) wireless standard maintained by the NFC Forum, enabling data exchange between devices; cyber tools use it to probe, emulate, or intercept contactless card and tag transactions. authenticator, Okta Verify for Linux, and malware proxy detection.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
Block access from known malware proxy networks by adding the MALWARE_PROXIES category to an Enhanced Dynamic Network Zone and denying it in the global session policy.
📍In the Admin Console, go to Security › Networks, open or create an Enhanced Dynamic Network Zone, add MALWARE_PROXIES to the excluded IP service categories, then go to Security › Global Session Policy and add a rule that denies access when the network zone matches.
Block remote-desktop originating traffic at the app sign-in policy level using the new REMOTE_DESKTOP IP service category.
📍In the Admin Console, go to Security › Networks, open or create an Enhanced Dynamic Network Zone, add REMOTE_DESKTOP to the excluded IP service categories, then open the target app's Sign-on Policy and add a rule denying access when the zone matches.
Register an MCP server from the OIN catalog to avoid manually entering connection details and immediately discover its available tools.
📍In the Admin Console, go to Applications › MCP Servers, click Add MCP Server, select Add from OIN catalog, locate the provider entry, choose Dynamic Client Registration (DCR) as the registration method, and click Test credentials and discover tools to verify the connection.
Adds REMOTE_DESKTOP IP service category to Enhanced Dynamic Network Zones, letting admins include or exclude remote-desktop traffic in global session and app sign-in policies for precise access control.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds MALWARE_PROXIES IP service category to Enhanced Dynamic Network Zones, powered by Okta CyberDefense, covering proxy services tied to malware and botnet activity (including 911 S5, NSOCKS, iProxy, and BHProxies).
Supports Dynamic Client Registration (DCR) when manually registering an MCP server — Okta automatically registers a client with the provider and populates credentials.
Enables adding MCP servers directly from an Okta Integration Network catalog entry, eliminating the need to enter connection details manually.
Adds tool discovery for MCP servers at registration time, letting admins test credentials and view available tools before completing setup.
+19 moreshow less
Adds NFC authenticator support for frontline workers on Windows shared workstations — users tap an NFC badge and enter a PIN to meet MFAMFAMulti-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. requirements without a phone, password, or shared account.
Extends Okta Verify with official Linux desktop support (Ubuntu 24.04 and 26.04), enabling phishing-resistant, hardware-backed Okta FastPass for Linux users.
Introduces the Okta Integration Wizard (OIW) to create and deploy custom app integrations configuring SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management., SCIMSCIMA standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave. provisioning, Entitlement Management, Universal Logout, API service integration, and custom API Integration Actions — reusable as a template across multiple app instances.
Adds unified identity for AI agents: admins can set an external identifier to enforce uniqueness, configure creation and matching criteria for imported AI agents, and preview imports before registration.
Adds Desktop MFA Factor Discovery for Windows, showing users only their enrolled MFA factors instead of a fixed list of all available factors.
Adds Low-Code Sign In Customization, letting admins modify text, colors, and images in the Sign-In Widget and Interstitial authentication using a JSON templating language with syntax highlighting and suggestions — no code editor required.
Logs failed WebAuthnWebAuthnA web standard that lets a browser prove possession of a passkey or hardware key to a website. It is the browser-facing part of FIDO2 sign-in. (FIDO2FIDO2The open standard behind passkeys and hardware security keys, where a website checks a signature from the user's device instead of a password. Because the key is bound to the site, phishing pages cannot use it.) enrollment attempts in the System Log under the user.mfa.factor.activate event with debug data including AAGUIDAAGUIDA 128-bit identifier embedded in a FIDO2/WebAuthn authenticator that identifies the make and model of the device, letting relying parties enforce authenticator policy without tracking individual users., isBackupEligible, and matched authenticator groups.
Supports high availability for the On-prem Connector for Generic Databases by allowing multiple Okta On-Premises SCIM Agents to be assigned to a single app instance.
Adds incremental imports for the On-prem Connector for Generic Databases, retrieving only users and entitlement assignments changed since the last successful import.
Adds entitlement import safeguards configurable per app using percentage-based or absolute count thresholds to prevent accidental removal of app roles or licenses on user unassignment, with an option to block imports that modify or delete entitlement schemas.
Enhances the Applications page with filtering by type and status, search by name or client ID, last-modified-date view, and CSV export for audit-ready reports.
Adds email notifications for Active DirectoryActive DirectoryMicrosoft's directory service for Windows networks that centralises authentication and authorisation; cyber tools target or integrate with it because it controls identity and access across most enterprise environments. and LDAPLDAPA protocol for querying and modifying directory services, standardized under RFC 4511, commonly used to look up users, groups, and attributes in corporate identity stores like Active Directory. agent disruption and recovery, configurable in the Admin Console.
Increases Access Request limits: users per task or question to 25 (from 10), entitlement bundles in an access level condition to 1,000 (from 100), groups in an access level condition to 1,000 (from 500), request type configuration lists per org to 250 (from 100), and request types per org to 750 (from 500).
Increases the maximum realm assignments per profile source from 30 to 100.
Adds provisioning support for WordPress, Ivanti, Progress Chef, Vercel, and Sophos Cloud integrations.
Updates MCP server registration UI with improved scope handling and tool visibility.
Updates the AI agent Client Registration tab to display authentication methods vertically with a Configure button linking to per-method configuration pages.
Replaces Okta On-prem SCIM Server agent with Okta On-prem SCIM agent, reducing dependencies and enabling new features.
Improves DBSSO device probing to use device-registered conditions from an app's sign-on policy instead of org-wide probing methods.
Adds REMOTE_DESKTOP IP service category to Enhanced Dynamic Network Zones, letting admins include or exclude remote-desktop traffic in global session and app sign-in policies for precise access control.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds MALWARE_PROXIES IP service category to Enhanced Dynamic Network Zones, powered by Okta CyberDefense, covering proxy services tied to malware and botnet activity (including 911 S5, NSOCKS, iProxy, and BHProxies).
Enables adding MCP servers directly from an Okta Integration Network catalog entry, eliminating the need to enter connection details manually.
Adds tool discovery for MCP servers at registration time, letting admins test credentials and view available tools before completing setup.
Adds NFC authenticator support for frontline workers on Windows shared workstations — users tap an NFC badge and enter a PIN to meet MFAMFAMulti-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. requirements without a phone, password, or shared account.
+6 moreshow less
Extends Okta Verify with official Linux desktop support (Ubuntu 24.04 and 26.04), enabling phishing-resistant, hardware-backed Okta FastPass for Linux users.
Introduces the Okta Integration Wizard (OIW) to create and deploy custom app integrations configuring SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management., SCIMSCIMA standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave. provisioning, Entitlement Management, Universal Logout, API service integration, and custom API Integration Actions — reusable as a template across multiple app instances.
Adds Low-Code Sign In Customization, letting admins modify text, colors, and images in the Sign-In Widget and Interstitial authentication using a JSON templating language with syntax highlighting and suggestions — no code editor required.
Adds entitlement import safeguards configurable per app using percentage-based or absolute count thresholds to prevent accidental removal of app roles or licenses on user unassignment, with an option to block imports that modify or delete entitlement schemas.
Adds email notifications for Active DirectoryActive DirectoryMicrosoft's directory service for Windows networks that centralises authentication and authorisation; cyber tools target or integrate with it because it controls identity and access across most enterprise environments. and LDAPLDAPA protocol for querying and modifying directory services, standardized under RFC 4511, commonly used to look up users, groups, and attributes in corporate identity stores like Active Directory. agent disruption and recovery, configurable in the Admin Console.
Adds provisioning support for WordPress, Ivanti, Progress Chef, Vercel, and Sophos Cloud integrations.
13 more in Everything
└──▷ BREAKING ON UPGRADE
!Okta On-prem SCIM Server agent has been replaced by Okta On-prem SCIM agent — existing deployments referencing the old agent name must migrate to the new Okta On-prem SCIM agent.
Explore iDenfy documentation for identity verification (KYC), business verification (KYB), AML screening, fraud prevention, and more.
iDenfy's Sprint 135 release adds Bank Card Verification and a Blocklist API endpoint, extends KYBKYBKnow Your Business — a regulatory compliance process for verifying the legal identity, ownership, and legitimacy of a business entity, used by cyber tools to screen counterparties or customers against fraud and sanctions risk. with field filtering and shared identity verification across companies, adds native-script CSV exports, automatic branding import from your website, and document-capture improvements including real-time framing feedback and expanded injection detection, while raising the iOS SDK's minimum deployment target to iOS 15.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
9 FEATURES0 OF 9 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Field filtering for KYB company endpointnew70how completely this was documenteddepth20/40specificity25/30actionability25/3070 / 100
Adds a fields parameter to the KYB company endpoint to return only the data fields you need.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Native-script data in KYC CSV exportnew60how completely this was documenteddepth25/40specificity20/30actionability15/3060 / 100
Adds an Original language data section to KYCKYCKnow Your Customer — a regulatory requirement that financial services verify the identity of their users before granting access, used by cyber tools handling payments or financial data to stay compliant. CSV reports, exporting document values in their native script as separate columns.
Document capture feedback and injection detection expansionimproved45how completely this was documenteddepth20/40specificity15/30actionability10/3045 / 100
Adds real-time framing feedback during document capture, and extends injection detection to images that did not go through the iDenfy capture flow (experimental).
iDenfy adds Bank Card Verification, Blocklist API, KYBKYBKnow Your Business — a regulatory compliance process for verifying the legal identity, ownership, and legitimacy of a business entity, used by cyber tools to screen counterparties or customers against fraud and sanctions risk. fields filtering, CSV native-script export, and branding auto-import in Sprint 135︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds a fields parameter to the KYB company endpoint to return only the data fields you need.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds a Blocklist API endpoint.
Adds Bank Card Verification capability.
Adds KYB shared identity verification across companies.
Adds an Original language data section to KYCKYCKnow Your Customer — a regulatory requirement that financial services verify the identity of their users before granting access, used by cyber tools handling payments or financial data to stay compliant. CSV reports, exporting document values in their native script as separate columns.
+6 moreshow less
Supports PNG logo uploads.
Enables branding themes to be prefilled from your website, pulling in colors and logo automatically.
Adds real-time framing feedback during document capture.
Extends injection detection to images that did not go through the iDenfy capture flow (experimental).
Adds a Recommended document badge in the iOS SDK (v9.2.2).
Adds iOS 27 support in the iOS SDK (v9.2.2).
Adds a fields parameter to the KYB company endpoint to return only the data fields you need.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds a Blocklist API endpoint.
Adds Bank Card Verification capability.
Adds KYB shared identity verification across companies.
Enables branding themes to be prefilled from your website, pulling in colors and logo automatically.
+1 moreshow less
Adds a Recommended document badge in the iOS SDK (v9.2.2).
5 more in Everything
└──▷ BREAKING ON UPGRADE
!The iOS SDK minimum deployment target is raised to iOS 15.
Adds defaultDocumentCamera and defaultLivenessCamera SDK options to the Web SDK, allowing the document and face-capture steps to open on the rear camera by default (e.g.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ for kiosk or operator-assisted flows).
Adds showDocumentCameraSwitchButton and showLivenessCameraSwitchButton SDK options to the Web SDK to hide the in-capture camera switcher and lock users to the chosen lens.
Adds defaultDocumentCamera and defaultLivenessCamera SDK options to the Web SDK, allowing the document and face-capture steps to open on the rear camera by default (e.g.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ for kiosk or operator-assisted flows).
Govern workforce access, deploy AI agents, and get work done with C1.
ConductorOne's biggest changes this window are infrastructure-level: EU data residency, a public REST APIREST APIA web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. for AI governance objects, Terraform support for MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. sources, and a breaking split of credential revocation from secret deletion — alongside persistent AI-generated reports, AI-assisted task diagnosis, and a string of access-review and campaign refinements.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
16 FEATURES6 OF 16 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Credential revoke decoupled from secret deletionbreaking90how completely this was documenteddepth30/40specificity30/30actionability30/3090 / 100
POST /api/v1/app-secrets-admin/revoke now queues a credential revoke separately from secret deletion, while DELETE /api/v1/secrets/{vault_id} only deletes the secret and no longer revokes its credential.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Service SDKs rename their Revoke method to Delete to match the new behavior.
Revoke a credential after deleting a shared secret — now two separate calls since deletion no longer implies revocation.
Spend-remedy task type and endpoint removalbreaking90how completely this was documenteddepth30/40specificity30/30actionability30/3090 / 100
GET /api/v1/tasks/{task_id}/spend-remedy-status has been removed — migrate to the task APIs. TYPE_SPEND_REMEDY = 7 is added as a new task action type, and JS/TS clients must handle spend-control revision values as strings; integrations with a closed list of task action types must handle the new type.
Saveable and reusable C1AI reportsnew80how completely this was documenteddepth30/40specificity25/30actionability25/3080 / 100
A Save report action in the AI assistant names and persists a report so it isn't lost between sessions. A new Platform > Reporting page lists all saved reports with rename, delete, refresh, and Edit with Report assistant controls, and each saved report has a Function tab to inspect the underlying logic and data sources behind its results.
Find and re-run a previously saved access report without hunting through conversation history.
📍Navigate to Platform › Reporting, locate the saved report by name, then select Refresh to re-run it against the latest data, or Edit with Report assistant to adjust its parameters in a conversation.
AI-assisted stuck task diagnosisnew75how completely this was documenteddepth30/40specificity20/30actionability25/3075 / 100
Super Admins can ask C1AI to diagnose a stuck, failed, or waiting task (e.g. 'why is task #4821 stuck?'); the assistant traces the task's approval and provisioning state, access-profile origin, app-account access, and connector handoff, then recommends whether to approve, deny, or retry, without taking disruptive action itself.
Diagnose a stuck provisioning task as a Super Admin without touching any live state.
📍In the C1 console, open the stuck task's detail page, then select Ask C1AI and type: 'Why is this task stuck and what should I do next?'
Diagnose a task that is stuck in provisioning without taking any disruptive action — useful before escalating or retrying.
📍In the C1AI assistant, type: 'why is task #4821 stuck?' The assistant traces the task's approval and provisioning state, access profile origin, app-account access, and connector handoff, then recommends whether to approve, deny, or retry.
EU data residency instancenew65how completely this was documenteddepth25/40specificity25/30actionability15/3065 / 100
A new EU data residency instance is selectable at domain registration, affecting all tenant-specific URLs including login, redirect URIs, API and webhook endpoints, MCP server, and CLI configuration.
Change history and justification for configuration changesnew65how completely this was documenteddepth25/40specificity25/30actionability15/3065 / 100
A Change history icon on configuration object detail pages (connectors, policies, entitlement routing rules, SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management., branding settings, AI Gateway spend controls) shows a before-and-after timeline of every change. Connector configuration changes can now optionally require a justification, captured alongside that history.
Set assignee step in Transformation rulesnew65how completely this was documenteddepth25/40specificity20/30actionability20/3065 / 100
A new Set assignee step in Automation > Transformation rules automatically assigns a matched access-review finding to a specific person, overriding any automatic assignee for those findings.
Automatically assign access-review findings to the right owner using a Transformation rule instead of manual triage.
📍In the C1 console, go to Automation › Transformation rules, open or create a rule, add a new step, select Set assignee, and specify the target user — this assignment will override any automatic assignee for matched findings.
Access review and campaign management improvementsimproved65how completely this was documenteddepth25/40specificity25/30actionability15/3065 / 100
Access-review revoke-task reviewer denial reasons are now automatically included in ticketing system templates, with new template variables available for custom templates. Campaign scope now expands to include users with pending (unaccepted) account invitations. Conflict monitors can handle groups of very different sizes (e.g., 90 and 11) as long as the combined total stays under 1,024 members. Access-review tables also gain a Resource description column, showing custom descriptions or connector-synced metadata as a fallback.
Public REST API for AI governance objectsnew60how completely this was documenteddepth20/40specificity25/30actionability15/3060 / 100
Classifiers, tool gates, classifier bindings, templates, and the agent classifier policy are now exposed through the public REST API, enabling programmatic management of AI governance configuration.
Terraform support for MCP sourcesnew55how completely this was documenteddepth20/40specificity20/30actionability15/3055 / 100
New Terraform resources let admins manage hosted and external MCP sources as code via C1's Terraform provider, covering source details, authentication, and tool enablement policy.
Apps and Entitlements tabs in My resourcesnew50how completely this was documenteddepth15/40specificity20/30actionability15/3050 / 100
The My resources page gains Apps and Entitlements tabs, consolidating groups, vaults, credential stores, secrets, apps, and entitlements into one view.
Explicit toolset grant required for MCP accessbreaking50how completely this was documenteddepth20/40specificity15/30actionability15/3050 / 100
MCP access control now requires an explicit toolset grant on the MCP server — app membership or an admin role alone no longer implies access, so existing setups relying on implicit access must be updated.
Safer handling of legacy name-only revoke criteriabreaking50how completely this was documenteddepth20/40specificity15/30actionability15/3050 / 100
A revoke criteria scoped only by a legacy resource-type name now fails the step instead of silently matching every app sharing that name; automations still relying on name-only matching must be re-scoped.
Unified MCP integration setup flowimproved45how completely this was documenteddepth15/40specificity15/30actionability15/3045 / 100
Registered MCP integrations, both catalog and external, are now unified into a single guided setup flow covering connection, access, tool approval, and authentication.
Agent-to-agent discovery over MCPnew40how completely this was documenteddepth15/40specificity15/30actionability10/3040 / 100
Customer agents connected to a C1 MCP endpoint can now discover and converse with c1aw agents, enabling agent-to-agent interaction through the MCP integration.
DELETE /api/v1/secrets/{vault_id} now deletes only the secret and no longer revokes its credential — use the new POST /api/v1/app-secrets-admin/revoke to queue a credential revoke separately. Service SDKs rename Revoke to Delete to match.
!
GET /api/v1/tasks/{task_id}/spend-remedy-status has been removed — migrate to the task APIs. JS/TS clients must handle spend-control revision values as strings, and integrations with a closed list of task action types must handle the new TYPE_SPEND_REMEDY = 7.
!
A revoke criteria scoped only by a legacy resource-type name now fails the step instead of silently matching every app sharing that name — re-scope any automation still relying on name-only matching.
ConductorOne adds EU data residency, saveable AI reports, REST APIREST APIA web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. for AI governance, MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Terraform support, and a POST /api/v1/app-secrets-admin/revoke credential-revoke endpoint.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Revoke a credential after deleting a shared secret — now two separate calls since deletion no longer implies revocation.
Diagnose a stuck provisioning task as a Super Admin without touching any live state.
📍In the C1 console, open the stuck task's detail page, then select Ask C1AI and type: 'Why is this task stuck and what should I do next?'
Automatically assign access-review findings to the right owner using a Transformation rule instead of manual triage.
📍In the C1 console, go to Automation › Transformation rules, open or create a rule, add a new step, select Set assignee, and specify the target user — this assignment will override any automatic assignee for matched findings.
Adds POST /api/v1/app-secrets-admin/revoke endpoint to queue credential revokes separately from secret deletion, replacing the previous combined behavior of DELETE /api/v1/secrets/{vault_id}.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Exposes classifiers, tool gates, classifier bindings, templates, and the agent classifier policy through the public REST API for AI governance management.
Introduces TYPE_SPEND_REMEDY = 7 as a new task action type; JS/TS clients must handle spend-control revision values as strings.
Adds Terraform resources for managing hosted and external MCP sources — including details, authentication, and tool enablement policy — as code via C1's Terraform provider.
Launches EU data residency instance, selectable at domain registration, affecting all tenant-specific URLs including login, redirect URIs, API and webhook endpoints, MCP server, and CLI configuration.
+14 moreshow less
Adds Save report action and a Platform > Reporting page where saved C1AI reports can be named, described, refreshed, and edited with the Report assistant.
Enables Super Admins to ask C1AI to diagnose a stuck, failed, or waiting task — tracing approvals, provisioning, access-profile origin, and connector handoff.
Adds a Change history icon to configuration object detail pages (connectors, policies, entitlement routing rules, SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management., branding settings, AI Gateway spend controls) showing a before-and-after timeline of every change.
Adds optional justification requirement for connector configuration changes, captured alongside change history.
Adds a Set assignee step to Transformation rules for automatically assigning a finding to a specific person.
Adds Apps and Entitlements tabs to the My resources page, consolidating groups, vaults, credential stores, secrets, apps, and entitlements in one view.
Adds agent-to-agent discovery: customer agents connected to a C1 MCP endpoint can now discover and converse with c1aw agents.
Changes MCP access control to require an explicit toolset grant on the MCP server — app membership or admin role alone no longer implies access.
Unifies registered MCP integrations (catalog and external) into a single guided setup flow covering connection, access, tool approval, and authentication.
Renders entitlement request forms inline in the Slack modal when requesting or extending access via the C1 app for Slack.
Includes access-review revoke-task reviewer denial reasons in ticketing system templates automatically, with new template variables available for custom templates.
Expands campaign scope to include users with pending (unaccepted) account invitations.
Allows conflict monitors to handle groups of very different sizes (e.g., 90 and 11) as long as the combined total stays under 1,024 members.
Adds a Resource description column to access-review tables, showing custom descriptions or connector-synced metadata as a fallback.
Adds POST /api/v1/app-secrets-admin/revoke endpoint to queue credential revokes separately from secret deletion, replacing the previous combined behavior of DELETE /api/v1/secrets/{vault_id}.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Exposes classifiers, tool gates, classifier bindings, templates, and the agent classifier policy through the public REST API for AI governance management.
Introduces TYPE_SPEND_REMEDY = 7 as a new task action type; JS/TS clients must handle spend-control revision values as strings.
Adds Terraform resources for managing hosted and external MCP sources — including details, authentication, and tool enablement policy — as code via C1's Terraform provider.
Launches EU data residency instance, selectable at domain registration, affecting all tenant-specific URLs including login, redirect URIs, API and webhook endpoints, MCP server, and CLI configuration.
+6 moreshow less
Adds Save report action and a Platform > Reporting page where saved C1AI reports can be named, described, refreshed, and edited with the Report assistant.
Enables Super Admins to ask C1AI to diagnose a stuck, failed, or waiting task — tracing approvals, provisioning, access-profile origin, and connector handoff.
Adds a Change history icon to configuration object detail pages (connectors, policies, entitlement routing rules, SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management., branding settings, AI Gateway spend controls) showing a before-and-after timeline of every change.
Adds optional justification requirement for connector configuration changes, captured alongside change history.
Adds a Set assignee step to Transformation rules for automatically assigning a finding to a specific person.
Adds agent-to-agent discovery: customer agents connected to a C1 MCP endpoint can now discover and converse with c1aw agents.
8 more in Everything
└──▷ BREAKING ON UPGRADE
!DELETE /api/v1/secrets/{vault_id} now deletes only the secret and no longer revokes its credential — use the new POST /api/v1/app-secrets-admin/revoke to queue a credential revoke separately. Service SDKs rename Revoke to Delete to match.
!GET /api/v1/tasks/{task_id}/spend-remedy-status has been removed — migrate to the task APIs. JS/TS clients must handle spend-control revision values as strings, and integrations with a closed list of task action types must handle the new TYPE_SPEND_REMEDY = 7.
!A revoke criteria scoped only by a legacy resource-type name now fails the step instead of silently matching every app sharing that name — re-scope any automation still relying on name-only matching.
JumpCloud makes it simple to manage Windows, Apple, Linux, and Android devices and to deliver secure access with SSO, MFA, Zero Trust, RADIUS, and more.
JumpCloud launched SaaS ManagementSaaS ManagementA category of software that tracks, governs, and optimises an organisation's portfolio of SaaS subscriptions, covering spend, access, and licence utilisation from a single control plane. for shadow-IT discovery and app governance, added a Windows Device Patch Report with CSV export, extended AI Assistant with a Knowledge Base and AI Gateway with MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. server discovery, and introduced new OAuth client authentication options for agents — alongside breaking API changes that move user reactivation to a POST endpoint and rename Dynamic Groups filter operators.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
14 FEATURES2 OF 14 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0101
OAuth client authentication types for agentsnew83how completely this was documenteddepth30/40specificity28/30actionability25/3083 / 100
An agent's Authentication tab now offers Client secret basic and Client secret post client authentication type options, controlling how the agent platform sends the client ID and secret when requesting an OAuth token from JumpCloud.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Client secret post is needed for platforms like Amazon Bedrock AgentCore that require credentials in the request body rather than the authorization header.
Match an agent's OAuth flow to Amazon Bedrock AgentCore, which requires credentials in the request body rather than the authorization header.
📍In the Admin Portal, open the agent's Authentication tab, and under client authentication type select Client secret post so credentials are sent in the request body when requesting a token from JumpCloud.
Register an AI agent and configure it with OAuth credentials so it can access SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. applications through AI Gateway — without touching any human user accounts.
📍1. Go to Identity Management › Agents and click + Add.
2. Enter the agent name, owner, and company email on the Details tab.
3. On the Authentication tab, generate OAuth client credentials; set client authentication type to Client secret post if your external platform (e.g. Amazon Bedrock AgentCore) sends credentials in the request body.
4. Under Identity Management › Agent Groups, create an Agent Group, add the agent, and assign SSO applications.
5. On the agent Applications tab, use Manage connections to authorize MCP servers on behalf of the agent.
Device Patch Report for Windowsnew83how completely this was documenteddepth30/40specificity28/30actionability25/3083 / 100
The Device Patch Report (Windows) shows per-device Installed, Pending, and Failed status for each Windows KB patch, with a preview of up to 500 rows in the portal and full CSV export of the complete result set.
Investigate patch compliance for a specific Windows device by previewing KB status in the portal, then downloading the full org dataset for reporting.
📍In the Admin Portal, go to Device Patch Report (Windows), review the Installed, Pending, and Failed KB status per device (up to 500 rows in preview), then click Download to export the complete result set as CSV.
Global MFA Requirement for MSP adminsnew81how completely this was documenteddepth28/40specificity25/30actionability28/3081 / 100
MSPMSPA managed service provider, a company that operates IT services for customers. It may manage systems, networks, backups or other ongoing technology needs. admins can enforce MFAMFAMulti-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. for all admins in the Multi-Tenant Portal via Account > Settings > Global MFA Requirement toggle, closing the gap where individual admin accounts might have MFA disabled.
Enforce Global MFA for all MSP admins in the Multi-Tenant Portal to close the gap where individual admin accounts might have MFA disabled.
📍In the Admin Portal, go to Account › Settings and enable the Global MFA Requirement toggle under the Global MFA Requirement section.
MCP server discovery and AI Gateway registrationnew75how completely this was documenteddepth25/40specificity25/30actionability25/3075 / 100
Under Access > AI & SaaSSaaSSoftware delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally. Management > Applications, a new MCP Connection column flags apps with a Discovered status; admins can review the discovered MCP servers and click Add MCP ServerMCP ServerA process that exposes tools, resources, and prompts over Anthropic's Model Context Protocol, letting an AI agent call external APIs or local services through a standardised interface. to register them in AI Gateway.
Check which managed applications have MCP servers discovered on devices, then connect one to AI Gateway — all without leaving the SaaS management view.
📍1. Go to Access › AI & SaaS Management › Applications.
2. Locate the MCP Connection column; look for apps showing Discovered.
3. Click the Discovered status to review the discovered MCP servers.
4. Click Add MCP Server to register the server in AI Gateway.
5. To review details later, select the application and click View next to MCP Connection in the right-hand menu.
Ad hoc command execution on devicesnew75how completely this was documenteddepth25/40specificity22/30actionability28/3075 / 100
Admins can run an ad hoc shell command on a specific managed device via Devices > select device > Commands > Run Ad Hoc Command, without pre-binding it to a command object, and view output immediately in a results panel.
Run an ad hoc remediation command on a specific managed device without pre-binding it to a command object.
📍In the Admin Portal, go to Devices › select a device › Commands › Run Ad Hoc Command, enter your shell command, and click Run to execute immediately and view output in the results panel.
Preview dynamic group membership changes before applyingnew72how completely this was documenteddepth25/40specificity22/30actionability25/3072 / 100
Dynamic Groups gain a 'Review membership changes before they take effect' option, letting admins preview membership updates — e.g. a group scoped by a Public IP Address rule — before they are applied.
Automatically keep a Remote Workers device group current without manual intervention by scoping membership to devices with a known public IP range.
📍In the Admin Portal, go to Device Groups › Create Group › set Type to Dynamic, add a rule for Public IP Address matching your corporate egress range, then enable 'Review membership changes before they take effect' to preview before applying.
Forced Re-authentication for SSO sessionsnew70how completely this was documenteddepth25/40specificity30/30actionability15/3070 / 100
Supports Forced Re-authentication via ForceAuthn='true' in SAMLSAMLA standard for passing signed identity assertions between a sign-in provider and an application. It lets a user sign in through their organization's identity provider. and prompt=login in OIDCOIDCOpenID Connect, a sign-in protocol built on OAuth 2.0. An application uses identity information from a trusted provider instead of maintaining a separate password for each user., prompting fresh credential entry even when an active session already exists.
RSS feeds for agent release notes and bug fixesnew63how completely this was documenteddepth20/40specificity18/30actionability25/3063 / 100
Admins can subscribe separately to an Agent Release Notes RSS Feed and a Bug Fixes RSS Feed from the JumpCloud Release Notes and Bug Fixes page, to receive operational updates automatically in an RSS reader.
Subscribe to only agent release notes and bug fix reports to keep a dedicated RSS reader channel scoped to operational changes.
📍1. Go to the JumpCloud Release Notes and Bug Fixes page.
2. Click Subscribe to Agent Release Notes RSS Feed to receive agent-specific updates.
3. Click Subscribe to Bug Fixes RSS Feed to receive bug fix reports.
4. Open your RSS reader and add the resulting feed URLs to begin receiving notifications automatically.
— Exact feed names and subscription steps given.Subscribe to New Feature and Product Update …
thinner coverage below
0900
Shared folder management and manual sync in Password Managernew52how completely this was documenteddepth22/40specificity18/30actionability12/3052 / 100
Admins can manage shared folder assignments and permissions from the Admin Portal in JumpCloud Password Manager, and end users can manually sync individual folders from the desktop app.
JumpCloud Go session auto-refreshimproved43how completely this was documenteddepth20/40specificity15/30actionability8/3043 / 100
JumpCloud Go sessions now automatically refresh on device login or unlock, removing additional verification prompts for JumpCloud-protected browser resources.
Multi-select and sorting in Password Manager desktop appimproved25how completely this was documenteddepth10/40specificity10/30actionability5/3025 / 100
Adds multi-select functionality and item sorting to the Password Manager desktop app.
The GET api/systemusers/reactivate/{id} endpoint is deprecated and now returns 404; all scripts, automations, and integrations must switch to POST https://console.jumpcloud.com/systemusers/reactivate/{id} with activation_email in the request body.
!
Dynamic Groups API memberQuery filter operators $le and $ge are deprecated; API requests must use $lte and $gte respectively (Admin Portal-managed Dynamic Groups are not affected).
!
The .appimage Linux build is no longer supported as of April 18, 2024; users must migrate to the RPM or Debian build.
JumpCloud: Adds a required install success exit code field when deploying Windows EXE updates via the Private Repository, so JumpCloud can confirm installation succeeded.
└──▷ HOW TO FIND IT
Investigate patch compliance for a specific Windows device by previewing KB status in the portal, then downloading the full org dataset for reporting.
📍In the Admin Portal, go to Device Patch Report (Windows), review the Installed, Pending, and Failed KB status per device (up to 500 rows in preview), then click Download to export the complete result set as CSV.
Match an agent's OAuth flow to Amazon Bedrock AgentCore, which requires credentials in the request body rather than the authorization header.
📍In the Admin Portal, open the agent's Authentication tab, and under client authentication type select Client secret post so credentials are sent in the request body when requesting a token from JumpCloud.
Ground AI Assistant in org-specific runbooks and SOPs so it can answer policy questions with attributed sources.
📍In the Admin Portal, navigate to AI Assistant, open the Knowledge Base section, and upload up to 25 internal documents (PDF, TXT, DOCX, or MD, max 10 MB each) — AI Assistant will cite the source document in any response that draws on uploaded content.
Adds Client secret basic and Client secret post client authentication type options on an agent's Authentication tab, controlling how the agent platform sends the client ID and secret when requesting an OAuth token from JumpCloud.
JumpCloud: Introduces a Linux Forbidden Services policy to remove unsupported service types and reduce security risk on Linux fleets.
└──▷ HOW TO FIND IT
Enforce Chrome security patches across every OS in your fleet with a single policy instead of per-OS rules.
📍In the Admin Portal, go to Device Management › Policies › New Policy, select Browser Patch Management and choose the Universal (macOS, Windows, Linux) policy type, configure the update schedule, and save.
Harden Linux fleets by disabling risky or unnecessary system services across all managed Linux devices.
📍In the Admin Portal, go to Device Management › Policies › New Policy, select Linux Forbidden Services, add the service names to block, assign the policy to the relevant Linux device group, and save.
Block macOS Ventura upgrades on managed devices until your org is ready to certify compatibility.
📍In the Admin Portal, go to Device Management › Policies › New Policy, select the macOS software management policy to Delay or Block macOS Ventura, assign it to your macOS device groups, and save.
Adds Premium Support Live Chat directly in the Admin Portal, automatically recognizing Premium Support status without requiring a PIN.
JumpCloud: Enables admins to manage shared folder assignments and permissions from the Admin Portal in JumpCloud Password Manager, and lets users manually sync individual folders from the desktop app.
└──▷ HOW TO FIND IT
Automatically keep a Remote Workers device group current without manual intervention by scoping membership to devices with a known public IP range.
📍In the Admin Portal, go to Device Groups › Create Group › set Type to Dynamic, add a rule for Public IP Address matching your corporate egress range, then enable 'Review membership changes before they take effect' to preview before applying.
Run an ad hoc remediation command on a specific managed device without pre-binding it to a command object.
📍In the Admin Portal, go to Devices › select a device › Commands › Run Ad Hoc Command, enter your shell command, and click Run to execute immediately and view output in the results panel.
Adds billing visibility for MSPMSPA managed service provider, a company that operates IT services for customers. It may manage systems, networks, backups or other ongoing technology needs. customers showing available and consumed user licenses and the ability to download their JumpCloud contract from the Multi-Tenant Portal.
JumpCloud: Adds manual application entry to SaaS ManagementSaaS ManagementA category of software that tracks, governs, and optimises an organisation's portfolio of SaaS subscriptions, covering spend, access, and licence utilisation from a single control plane. so admins can track, warn, and block access to apps before automatic discovery runs.
└──▷ TRY IT
Reactivate a user account using the new POST endpoint after migrating away from the deprecated GET request.
Enforce Global MFAMFAMulti-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. for all MSPMSPA managed service provider, a company that operates IT services for customers. It may manage systems, networks, backups or other ongoing technology needs. admins in the Multi-Tenant Portal to close the gap where individual admin accounts might have MFA disabled.
📍In the Admin Portal, go to Account › Settings and enable the Global MFA Requirement toggle under the Global MFA Requirement section.
Launches SaaSSaaSSoftware delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally. Management, providing discovery and tracking of SaaS app use via the JumpCloud Go browser extension, shadow-IT categorization, customizable warning/blocking messaging, and licensing information tracking.
Enables JumpCloud Go sessions to automatically refresh on device login or unlock, removing additional verification prompts for JumpCloud-protected browser resources.
Adds inactivity timer to Remote Assist app.
Adds multi-select functionality and item sorting to the Password Manager desktop app.
JumpCloud Go is no longer required at the organization level for SaaS Management app discovery; the JumpCloud Go browser extension alone suffices for end users.
Launches SaaSSaaSSoftware delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally. Management, providing discovery and tracking of SaaS app use via the JumpCloud Go browser extension, shadow-IT categorization, customizable warning/blocking messaging, and licensing information tracking.
4 more in Everything
└──▷ BREAKING ON UPGRADE
!The GET api/systemusers/reactivate/{id} endpoint is deprecated and now returns 404; all scripts, automations, and integrations must switch to POST https://console.jumpcloud.com/systemusers/reactivate/{id} with activation_email in the request body.
!Dynamic Groups API memberQuery filter operators $le and $ge are deprecated; API requests must use $lte and $gte respectively (Admin Portal-managed Dynamic Groups are not affected).
JumpCloud: Adds MTP support in the Customer Portal — MTP Admins can access, view, and create support cases across all managed tenant organizations.
Supports Forced Re-authentication via ForceAuthn='true' in SAMLSAMLA standard for passing signed identity assertions between a sign-in provider and an application. It lets a user sign in through their organization's identity provider. and prompt=login in OIDCOIDCOpenID Connect, a sign-in protocol built on OAuth 2.0. An application uses identity information from a trusted provider instead of maintaining a separate password for each user., prompting fresh credential entry even when an active session exists.
Adds macOS Dock Settings and Items policy updates and Lock Screen (Screen Saver) policy enhancements for managed macOS devices.
Supports Forced Re-authentication via ForceAuthn='true' in SAMLSAMLA standard for passing signed identity assertions between a sign-in provider and an application. It lets a user sign in through their organization's identity provider. and prompt=login in OIDCOIDCOpenID Connect, a sign-in protocol built on OAuth 2.0. An application uses identity information from a trusted provider instead of maintaining a separate password for each user., prompting fresh credential entry even when an active session exists.
JumpCloud: Adds Client secret basic and Client secret post client authentication type options on an agent's Authentication tab, controlling how OAuth client credentials are sent when requesting tokens from JumpCloud.
└──▷ HOW TO FIND IT
Register an AI agent and configure it with OAuth credentials so it can access SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. applications through AI Gateway — without touching any human user accounts.
📍1. Go to Identity Management › Agents and click + Add.
2. Enter the agent name, owner, and company email on the Details tab.
3. On the Authentication tab, generate OAuth client credentials; set client authentication type to Client secret post if your external platform (e.g. Amazon Bedrock AgentCore) sends credentials in the request body.
4. Under Identity Management › Agent Groups, create an Agent Group, add the agent, and assign SSO applications.
5. On the agent Applications tab, use Manage connections to authorize MCP servers on behalf of the agent.
Check which managed applications have MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. servers discovered on devices, then connect one to AI Gateway — all without leaving the SaaSSaaSSoftware delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally. management view.
📍1. Go to Access › AI & SaaS Management › Applications.
2. Locate the MCP Connection column; look for apps showing Discovered.
3. Click the Discovered status to review the discovered MCP servers.
4. Click Add MCP Server to register the server in AI Gateway.
5. To review details later, select the application and click View next to MCP Connection in the right-hand menu.
Introduces the Device Patch Report (Windows) in JumpCloud Reports, providing per-device visibility into KB patch installation status (Installed, Pending, Failed) with preview of up to 500 rows and full CSV export.
Adds in-place version updating for custom applications in the Private Repository via Update Version on the application's Details tab, including EXE install success exit code configuration for Windows.
Introduces the Device Patch Report (Windows) in JumpCloud Reports, providing per-device visibility into KB patch installation status (Installed, Pending, Failed) with preview of up to 500 rows and full CSV export.
Activate Password Manager in the EU region to ensure credentials are stored and synced within EU infrastructure.
📍On the desktop app activation page, select EU as your region before entering your activation code. For the browser extension, select EU on the pairing page before pairing.
└──▷ BREAKING ON UPGRADE
!The .appimage Linux build is no longer supported as of April 18, 2024; users must migrate to the RPM or Debian build.
Clerk's biggest ship this window is a full command-line workflow for agent-driven, zero-account Next.js setup, alongside GA of Client ID Metadata DocumentsClient ID Metadata DocumentsOAuth 2.0 documents hosted at a client's own URL that declare its identity and redirect URIs, letting authorization servers fetch and verify client metadata without manual registration. with new admission controls and a dedicated SMSSMSShort Message Service, the protocol built into cellular networks for sending text messages between phones; cyber tools use it for alerting, two-factor authentication delivery, or phishing simulation over mobile channels. delivery logs view.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
The easiest way to add authentication and user management to your application. Purpose-built for React, Next.js, Remix, and “The Modern Web”.
Clerk's biggest ship this window is a full command-line workflow for agent-driven, zero-account Next.js setup, alongside GA of Client ID Metadata DocumentsClient ID Metadata DocumentsOAuth 2.0 documents hosted at a client's own URL that declare its identity and redirect URIs, letting authorization servers fetch and verify client metadata without manual registration. with new admission controls and a dedicated SMSSMSShort Message Service, the protocol built into cellular networks for sending text messages between phones; cyber tools use it for alerting, two-factor authentication delivery, or phishing simulation over mobile channels. delivery logs view.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
3 FEATURES2 OF 3 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0101
Clerk CLI for agent-driven project setupnew95how completely this was documenteddepth35/40specificity30/30actionability30/3095 / 100
npx -y clerk@latest init provisions a claimable Clerk application, writes NEXT_PUBLIC_CLERK_PUBLISHABLE_KEY and CLERK_SECRET_KEY to .env.local, and configures the SDK, <ClerkProvider>, middleware, and auth routes with no Clerk account required; init --app <application_id> wires an existing application in instead of provisioning a new one.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ apps list --json enumerates existing applications by name and ID, enable orgs turns on organizations on a not-yet-claimed application, and config patch updates configuration on a not-yet-claimed application. The generated middleware file is named proxy.ts on Next.js 16+ and middleware.ts on Next.js 15 and below (identical contents), the CLI runs via npx -y clerk@latest, pnpm dlx clerk@latest, bunx clerk@latest, or yarn dlx clerk@latest (Yarn 2+), and it detects agent environments to run init non-interactively so no keys pass through the conversation.
Bootstrap Clerk in a new or existing Next.js project without a Clerk account — keys are written to .env.local automatically.
$ npx -y clerk@latest init
Connect a project to an existing Clerk application by choosing from all applications visible to the signed-in account.
$ npx -y clerk@latest apps list --json
# Review names and IDs, then:
npx -y clerk@latest init --app <application_id>
Enable organizations on a freshly provisioned, not-yet-claimed application before handing it to the user to claim.
$ npx -y clerk@latest enable orgs
— Full set of runnable CLI commands and flags namedproduct docs
0202
Client ID Metadata Documents reach GA with admission controlsnew75how completely this was documenteddepth30/40specificity25/30actionability20/3075 / 100
Client ID Metadata Documents (CIMDCIMDA text-based Short Message Service protocol from Nokia for exchanging SMS messages between applications and SMS centers, used to build tools that send, receive, or test carrier messaging flows.) are now generally available for every Clerk application, letting MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. and other public OAuth clients connect with a URL-based identity without a support request. Operators can further restrict OAuth flows via a new Client admission control set to Pre-registered clients only, and enable CIMD in authorization server metadata via a Publish CIMD support toggle under Client onboarding on the OAuth applications settings page.
Lock your MCP server's OAuth flow so only clients you have explicitly reviewed can authenticate, using CIMD admission controls.
📍In the Clerk Dashboard, go to OAuth applications settings › Client onboarding, enable Publish CIMD support, then set Client admission to Pre-registered clients only and add trusted client ID URLs from the Applications tab.
SMS delivery event logsnew75how completely this was documenteddepth30/40specificity25/30actionability20/3075 / 100
Application Logs now include sms.accepted, sms.delivered, sms.failed, sms.undeliverable, and sms.unconfirmed SMS delivery events, with a normalized reason field (e.g. invalid_phone_number, destination_unreachable, rate_limited) on failure events. A dedicated SMS logs view lets you filter by event type or destination phone number and see full per-message trace timelines.
Investigate why a user did not receive an SMS verification code by filtering the SMS logs to only failed delivery events for their number.
📍In the Clerk Dashboard, go to Logs › SMS logs view, filter by event type sms.failed, then enter the destination phone number to pull up that recipient's full delivery trace.
Clerk adds Client ID Metadata DocumentsClient ID Metadata DocumentsOAuth 2.0 documents hosted at a client's own URL that declare its identity and redirect URIs, letting authorization servers fetch and verify client metadata without manual registration. (GA) and SMSSMSShort Message Service, the protocol built into cellular networks for sending text messages between phones; cyber tools use it for alerting, two-factor authentication delivery, or phishing simulation over mobile channels. delivery event logs with per-event failure reasons︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
Investigate why a user did not receive an SMS verification code by filtering the SMS logs to only failed delivery events for their number.
📍In the Clerk Dashboard, go to Logs › SMS logs view, filter by event type sms.failed, then enter the destination phone number to pull up that recipient's full delivery trace.
Lock your MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. server's OAuth flow so only clients you have explicitly reviewed can authenticate, using CIMDCIMDA text-based Short Message Service protocol from Nokia for exchanging SMS messages between applications and SMS centers, used to build tools that send, receive, or test carrier messaging flows. admission controls.
📍In the Clerk Dashboard, go to OAuth applications settings › Client onboarding, enable Publish CIMD support, then set Client admission to Pre-registered clients only and add trusted client ID URLs from the Applications tab.
Adds sms.accepted, sms.delivered, sms.failed, sms.undeliverable, and sms.unconfirmed SMS delivery events to Application Logs, with a normalized reason field (e.g.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ invalid_phone_number, destination_unreachable, rate_limited) on failure events.
Adds a dedicated SMS logs view that lets you filter SMS delivery events by event type (e.g. sms.failed) or destination phone number, with full per-message trace timelines.
Adds Client admission control to CIMD settings, allowing operators to restrict OAuth flows to pre-reviewed clients by setting Client admission to Pre-registered clients only.
Adds Publish CIMD support toggle to the OAuth applications settings page under Client onboarding, enabling CIMD in the authorization server metadata.
Client ID Metadata DocumentsClient ID Metadata DocumentsOAuth 2.0 documents hosted at a client's own URL that declare its identity and redirect URIs, letting authorization servers fetch and verify client metadata without manual registration. (CIMDCIMDA text-based Short Message Service protocol from Nokia for exchanging SMS messages between applications and SMS centers, used to build tools that send, receive, or test carrier messaging flows.) are now generally available for all Clerk applications, enabling URL-based OAuth client identity.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Secure, scalable, and highly available authentication and user management for any app.
Okta expanded its AI Agent security suite with seven new capabilities spanning discovery, runtime enforcement, connection governance, and access reviews for AI agents.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
7 FEATURES0 OF 7 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Kill Switch expanded to Agent Gatewayimproved56how completely this was documenteddepth30/40specificity16/30actionability10/3056 / 100
Extends the existing Kill Switch to the Agent Gateway runtime layer, enabling revocation of every active token held by a compromised agent and termination of every session in flight at the moment of deactivation.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Agent SSO via Cross App Accessnew52how completely this was documenteddepth26/40specificity16/30actionability10/3052 / 100
Extends Cross App Access to all SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. customers, allowing non-expiring keys to be swapped for short-lived, identity-governed tokens to reduce user consent fatigue.
Agent Gateway runtime enforcementnew51how completely this was documenteddepth28/40specificity15/30actionability8/3051 / 100
Agent Gateway is a runtime enforcement point that sits in the execution path between an agent and its tool calls, enforcing policy and logging every interaction.
Okta for AI Agents adds shadow endpoint discovery, Agent Gateway runtime enforcement, agent-to-agent connection rules, and visual Configuration Designer.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds Shadow AI Agent Discovery for Endpoints, which surfaces unmanaged AI agents running on employee devices so they can be discovered and registered before becoming governance blind spots.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds Agent Gateway, a runtime enforcement point that sits in the execution path between an agent and its tool calls, enforcing policy and logging every interaction.
Adds Agent-to-AgentAgent-to-AgentAgent2Agent, an open protocol started by Google for AI agents from different vendors to discover each other, delegate tasks and exchange results. It complements MCP, which connects an agent to tools. Connections, which sets rules for which agents can call other agents, scopes what each agent can access, and captures the handoff in an auditable chain.
Adds Configuration Designer, a visual interface for mapping agent-to-resource connections so that each handoff is governed, scoped, and auditable.
Expands the Kill Switch to the Agent Gateway runtime layer, enabling revocation of every active token held by a compromised agent and termination of every session in flight at the moment of deactivation.
+2 moreshow less
Adds Agent SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management., extending Cross App Access to all SSO customers and allowing non-expiring keys to be swapped for short-lived, identity-governed tokens to reduce user consent fatigue.
Adds Resource Access Certifications, which periodically reviews agent resource connections over time to help prevent standing and excessive permissions.
Adds Shadow AI Agent Discovery for Endpoints, which surfaces unmanaged AI agents running on employee devices so they can be discovered and registered before becoming governance blind spots.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds Agent Gateway, a runtime enforcement point that sits in the execution path between an agent and its tool calls, enforcing policy and logging every interaction.
Adds Agent-to-AgentAgent-to-AgentAgent2Agent, an open protocol started by Google for AI agents from different vendors to discover each other, delegate tasks and exchange results. It complements MCP, which connects an agent to tools. Connections, which sets rules for which agents can call other agents, scopes what each agent can access, and captures the handoff in an auditable chain.
Adds Configuration Designer, a visual interface for mapping agent-to-resource connections so that each handoff is governed, scoped, and auditable.
Adds Agent SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management., extending Cross App Access to all SSO customers and allowing non-expiring keys to be swapped for short-lived, identity-governed tokens to reduce user consent fatigue.
+1 moreshow less
Adds Resource Access Certifications, which periodically reviews agent resource connections over time to help prevent standing and excessive permissions.
Discover the latest features, improvements, and updates to Ory.
Ory Network now lets workspaces register named contacts for technical, business, security, and privacy roles.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
1 FEATURE0 OF 1 FEATUREmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Workspace contact roles in Ory Networknew48how completely this was documenteddepth15/40specificity18/30actionability15/3048 / 100
Ory Network workspaces can register technical, business, security, and privacy contacts so Ory knows who to reach for each purpose.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Contacts are set from the workspace Settings page in the Ory Network console.
Assign contacts for each role in a workspace so the right person is reached for security incidents or billing questions.
📍In the Ory Network console, open your workspace, go to Settings, and fill in the technical, business, security, and privacy contact fields.
SandboxAQ AQtive Guard is a quantum-safe cryptography tool that protects against quantum computing threats to encryption.
AQtive Guard added support for deploying its on-premises packages to RHELRHELRed Hat Enterprise Linux, a commercially supported Linux distribution maintained by Red Hat, chosen by cyber tools for its long support lifecycle, certified hardware compatibility, and enterprise deployment prevalence. 10.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
1 FEATURE0 OF 1 FEATUREmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
RHEL 10 support for on-premises packagesnew35how completely this was documenteddepth10/40specificity15/30actionability10/3035 / 100
AQtive Guard on-premises packages now support RHEL 10 as a deployment target.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
AQtive Guard on-premises packages now available for RHELRHELRed Hat Enterprise Linux, a commercially supported Linux distribution maintained by Red Hat, chosen by cyber tools for its long support lifecycle, certified hardware compatibility, and enterprise deployment prevalence. 10.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Ubiq expanded structured encryption dataset coverage across nearly every client library, shipped a beta Rust SDK, a Kong API gateway plugin, and Apache AirflowApache AirflowAn open-source workflow orchestration platform maintained by the Apache Software Foundation that lets developers schedule, monitor, and chain tasks as directed acyclic graphs, making it useful for automating data pipelines. operators, and added identity-provider and SIEMSIEMSecurity information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents. depth to its access-governance dashboard.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Learn how Ubiq discovers sensitive data, maps identity-to-data access, and enforces protection policies across applications, databases, APIs, and AI.
Ubiq expanded structured encryption dataset coverage across nearly every client library, shipped a beta Rust SDK, a Kong API gateway plugin, and Apache AirflowApache AirflowAn open-source workflow orchestration platform maintained by the Apache Software Foundation that lets developers schedule, monitor, and chain tasks as directed acyclic graphs, making it useful for automating data pipelines. operators, and added identity-provider and SIEMSIEMSecurity information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents. depth to its access-governance dashboard.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
17 FEATURES1 OF 17 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Structured encryption for integers, dates, tokens, and strings across client librariesnew93how completely this was documenteddepth38/40specificity30/30actionability25/3093 / 100
The JavaScript library gains async structured encryption via EncryptNumberAsync, DecryptNumberAsync, and encryptNumberForSearchAsync for 32-bit (−99,999,999 to 99,999,999) and 64-bit (−9,999,999,999,999,999 to 9,999,999,999,999,999) integer datasets; EncryptDateTimeAsync, DecryptDateTimeAsync, and encryptDateTimeForSearchAsync for DateTime values (1653-02-10 to 2286-11-20 UTC); EncryptDateAsync, DecryptDateAsync, and encryptDateForSearchAsync for Date-only values; EncryptAsync, DecryptAsync, and encryptForSearchAsync for Token datasets of 64 characters (input up to 40 chars, base62 output) and 128 characters (input up to 80 chars, base62 output); and the same methods for generic string datasets with base32 or base64 encoding and configurable padding.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Objects are built via the new buildStructuredAsync method on CryptographyBuilder. This dataset type support (int32, int64, date, datetime, token 64/128-byte, and generic strings with Base32/Base64/no encoding) was also extended across the C, Node.js, Python, PHP, .NET, and Go libraries.
Encrypt a 32-bit integer field (e.g. an account ID) so it remains searchable in a database without exposing plaintext values.
— Names every method, dataset type, and exact numeric rangessnapshot-20260922
0200
Airflow operators for structured encryption in DAGsnew88how completely this was documenteddepth30/40specificity28/30actionability30/3088 / 100
Adds UbiqEncryptOperator and UbiqDecryptOperator for Apache Airflow to protect data inside DAGs. Each accepts a credentials parameter (via ubiq.configCredentials()), a data_task parameter referencing a prior task's task_id, and a dataset_names list mapping column positions to Ubiq dataset names, with empty strings for columns left unencrypted.
Encrypt specific columns (SSN, Birthdate) pulled from BigQueryBigQueryA serverless, cloud-hosted analytical database from Google that runs SQL queries across massive datasets without managing infrastructure, giving cyber tools scalable storage and fast querying over large volumes of log or event data. in a DAGDAGA directed acyclic graph — a data structure of nodes connected by one-way edges with no cycles — used by tools to model task pipelines or data flows where execution order and dependencies must be enforced without loops., then decrypt them in a downstream task — leaving other columns untouched.
— Full runnable DAG example with all parameter namessnapshot-20260922
0300
Custom metadata on usage recordsnew75how completely this was documenteddepth25/40specificity25/30actionability25/3075 / 100
Adds addReportingUserDefinedMetadata method accepting a JSON string (max 1,024 characters) to attach custom metadata to usage records on structured and conventional encryption objects, e.g. tagging records with an application or tenant identifier for audit correlation.
Attach custom audit metadata to usage records so SOCSOCA security operations center, the team or function that monitors threats, investigates alerts and coordinates incident response. Its work can be internal, outsourced or shared. teams can correlate encryption activity with a specific application or tenant.
text
const ubiqEncryptDecrypt = await (new ubiq.CryptographyBuilder())
  .withCredentialsObject(credentials)
  .withConfigurationObject(configuration)
  .buildStructuredAsync();

ubiqEncryptDecrypt.addReportingUserDefinedMetadata('{"app":"payments-service","tenant":"acme-corp"}');
— Named method, limit, and a concrete use caseproduct docs
0400
Key number introspection in Go librarynew75how completely this was documenteddepth25/40specificity25/30actionability25/3075 / 100
Adds CipherAndKeyNumber, GetCurrentKeyNumber, and GetKeyNumber functions to the Go library to return the key number behind a ciphertext without decrypting it, useful for key rotation auditing.
Inspect the key number behind a ciphertext in Go without decrypting, useful for key rotation auditing.
go
keyNum, err := ubiq.GetKeyNumber(ciphertext)
— Three named functions plus a runnable call and use casesnapshot-20260922
0500
Dataset cache prefetch in PHP librarynew72how completely this was documenteddepth25/40specificity22/30actionability25/3072 / 100
Adds new loadCache function to the PHP library to prefetch dataset configuration and encryption keys for many datasets in a single call, reducing first-use latency.
Warm up all dataset keys at PHP application startup with loadCache to eliminate per-request key-fetch latency when encrypting across many datasets.
php
$ubiq->loadCache($datasetNames);
— Named function with runnable one-line call and stated benefitsnapshot-20260922
0601
Rust SDK (Beta)new68how completely this was documenteddepth25/40specificity25/30actionability18/3068 / 100
Adds a new Ubiq Rust SDK (Beta), available on crates.io as ubiq-rust, supporting structured and unstructured encryption, integer and date/time datasets, encrypt_for_search, and key zeroization.
Use the new Rust SDK to encrypt a sensitive field with structured encryption in a Rust service — install the crate then call encrypt on a dataset.
toml
[dependencies]
ubiq-rust = "1.0.0"
— Names crate, capabilities, but no full usage samplesnapshot-20260922
0700
IDP-based credential creationnew67how completely this was documenteddepth22/40specificity20/30actionability25/3067 / 100
Adds UbiqFactory.createCredentialsWithIdp for creating credentials using an identity provideridentity providerA service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. (IDPIDPA service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems.) via <username>, <password>, and <host>, enabling authentication through an SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management.-enforced identity provider instead of static API keys.
Authenticate via an identity provider instead of static API keys, useful in SSO-enforced enterprise environments.
— Named factory method with its parameters and use caseproduct docs
thinner coverage below
0800
Dashboard Integrations page for IDP and SIEMimproved59how completely this was documenteddepth22/40specificity22/30actionability15/3059 / 100
Updates the Dashboard Integrations page to configure IDP and SIEM connections in a single location, with support for self-signed IDPs, IDP group-to-Access Group mapping, and SCIMSCIMA standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave. provisioning.
— Names a UI location and three specific capabilitiessnapshot-20260922
0900
Kong API gateway plugin for tokenizationnew52how completely this was documenteddepth22/40specificity20/30actionability10/3052 / 100
Adds a new Ubiq plugin for the Kong API gateway providing field-level tokenization and detokenization of JSON request and response bodies with no application changes.
— Describes mechanism but no config example or endpointsnapshot-20260922
1000
Access Graph identity-to-dataset tracingimproved50how completely this was documenteddepth20/40specificity18/30actionability12/3050 / 100
Expands the Access Graph to include IDP groups and filter related nodes in both directions, enabling access tracing from either an identity or a dataset.
— Describes new traversal direction but no exact UI pathsnapshot-20260922
1100
IDP and SCIM attribution in Security Historyimproved50how completely this was documenteddepth20/40specificity20/30actionability10/3050 / 100
Adds IDP identity attribution to Security History events, records SCIM sync and attribute-mapping failures, and shows Access Group in event details.
Grafana Loki SIEM integrationnew46how completely this was documenteddepth18/40specificity18/30actionability10/3046 / 100
Adds Grafana Loki as a SIEM destination for Ubiq activity and usage events, available to Enterprise customers alongside existing Splunk support.
— Names the destination and audience but no setup detailsnapshot-20260922
1300
Go input validation against dataset character setimproved43how completely this was documenteddepth18/40specificity15/30actionability10/3043 / 100
Adds improved input validation to the Go library — input is checked against the dataset character set before encryption, returning a clear error on mismatch.
— States mechanism but no error format or code samplesnapshot-20260922
1400
.NET FF1 update to BITLENimproved41how completely this was documenteddepth18/40specificity18/30actionability5/3041 / 100
Updates .NET structured encryption to use the BITLEN function in place of LOG, per NIST's updated FF1 recommendation.
— Names the function swap but no user-facing actionsnapshot-20260922
1500
Documented multithreading behavior for CryptographyBuilderimproved41how completely this was documenteddepth18/40specificity15/30actionability8/3041 / 100
Documents multithreaded-environment behavior: CryptographyBuilder objects are serialized and copied between Node.js worker threads rather than shared, requiring separate create/destroy cycles per thread.
— Explains behavior but is documentation-only, no exampleproduct docs
1600
Search and multi-select in Dataset Association dropdownimproved40how completely this was documenteddepth15/40specificity15/30actionability10/3040 / 100
Adds search and multi-select to the Dataset Association dropdown, and displays maximum input length for generic string datasets.
New reference docs and integration guidesnew38how completely this was documenteddepth12/40specificity18/30actionability8/3038 / 100
Adds new reference documentation for each structured dataset type (Date & Time, Date, Integer, Token, Formatted String, and Generic String) and new integration guides for Apache Airflow and Self-Signed IDP authentication.
Ubiq adds a Rust SDK, Kong gateway plugin, Airflow operators, Grafana Loki integration, and expanded dataset types across all client libraries.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ USE IT
Use the new Rust SDK to encrypt a sensitive field with structured encryption in a Rust service — install the crate then call encrypt on a dataset.
Cargo.toml
[dependencies]
ubiq-rust = "1.0.0"
Warm up all dataset keys at PHP application startup with loadCache to eliminate per-request key-fetch latency when encrypting across many datasets.
php
$ubiq->loadCache($datasetNames);
Inspect the key number behind a ciphertext in Go without decrypting, useful for key rotation auditing.
go
keyNum, err := ubiq.GetKeyNumber(ciphertext)
Adds new loadCache function to the PHP library to prefetch dataset configuration and encryption keys for many datasets in a single call, reducing first-use latency.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds new CipherAndKeyNumber, GetCurrentKeyNumber, and GetKeyNumber functions to the Go library to return the key number behind a ciphertext without decrypting it.
Adds new Ubiq Rust SDK (Beta) — available on crates.io as ubiq-rust — supporting structured and unstructured encryption, integer and date/time datasets, encrypt_for_search, and key zeroization.
Adds a new Ubiq plugin for the Kong API gateway providing field-level tokenization and detokenization of JSON request and response bodies with no application changes.
Adds new Ubiq encrypt and decrypt operators for Apache AirflowApache AirflowAn open-source workflow orchestration platform maintained by the Apache Software Foundation that lets developers schedule, monitor, and chain tasks as directed acyclic graphs, making it useful for automating data pipelines. to protect data inside Airflow DAGs.
+10 moreshow less
Adds Grafana Loki as a SIEMSIEMSecurity information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents. destination for Ubiq activity and usage events (Enterprise customers; alongside existing Splunk support).
Expands dataset type support across C, Node.js, Python, PHP, .NET, and Go libraries to include int32, int64, date, datetime, token (64/128-byte), and generic strings with Base32, Base64, or no encoding.
Adds improved input validation to the Go library — input is checked against the dataset character set before encryption, returning a clear error on mismatch.
Updates .NET structured encryption to use the BITLEN function in place of LOG, per NIST's updated FF1 recommendation.
Updates the Dashboard Integrations page to configure IDPIDPA service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. and SIEM connections in a single location, with support for self-signed IDPs, IDP group-to-Access Group mapping, and SCIMSCIMA standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave. provisioning.
Expands the Access Graph to include IDP groups and filter related nodes in both directions, enabling access tracing from either an identity or a dataset.
Adds IDP identity attribution to Security History events, records SCIM sync and attribute-mapping failures, and shows Access Group in event details.
Adds search and multi-select to the Dataset Association dropdown, and displays maximum input length for generic string datasets.
Adds new reference documentation for each structured dataset type: Date & Time, Date, Integer, Token, Formatted String, and Generic String.
Adds new integration guides for Apache Airflow and Self-Signed IDP authentication.
Adds new loadCache function to the PHP library to prefetch dataset configuration and encryption keys for many datasets in a single call, reducing first-use latency.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds new CipherAndKeyNumber, GetCurrentKeyNumber, and GetKeyNumber functions to the Go library to return the key number behind a ciphertext without decrypting it.
Adds new Ubiq Rust SDK (Beta) — available on crates.io as ubiq-rust — supporting structured and unstructured encryption, integer and date/time datasets, encrypt_for_search, and key zeroization.
Adds a new Ubiq plugin for the Kong API gateway providing field-level tokenization and detokenization of JSON request and response bodies with no application changes.
Adds new Ubiq encrypt and decrypt operators for Apache AirflowApache AirflowAn open-source workflow orchestration platform maintained by the Apache Software Foundation that lets developers schedule, monitor, and chain tasks as directed acyclic graphs, making it useful for automating data pipelines. to protect data inside Airflow DAGs.
+3 moreshow less
Adds Grafana Loki as a SIEMSIEMSecurity information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents. destination for Ubiq activity and usage events (Enterprise customers; alongside existing Splunk support).
Adds new reference documentation for each structured dataset type: Date & Time, Date, Integer, Token, Formatted String, and Generic String.
Adds new integration guides for Apache Airflow and Self-Signed IDP authentication.
The leading data and AI security platform that proactively reduces risk, enforces policies, and stops active threats with our AI-native automation.
Varonis expanded its integration footprint this window with new monitoring for GitHub Enterprise Cloud, Jira permission visibility, Confluence historical-content scanning, and self-service Snowflake PrivateLinkPrivateLinkAn AWS networking feature that exposes a service over a private endpoint inside a VPC, so traffic never traverses the public internet, giving cyber tools a way to integrate with cloud services without opening public routes. configuration, alongside Private Cloud Data Collector improvements for secret management and TerraformTerraformAn open-source infrastructure-as-code tool by HashiCorp that provisions cloud and on-premises resources through declarative configuration files, letting cyber tools automate and version-control their deployment environments. deployment plus customizable on-demand scan prioritization.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
6 FEATURES0 OF 6 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Snowflake PrivateLink configuration in integration wizardnew70how completely this was documenteddepth30/40specificity25/30actionability15/3070 / 100
Adds support for configuring Snowflake integrations using AWS PrivateLinkAWS PrivateLinkAn AWS networking feature that exposes a service over a private VPC endpoint rather than the public internet, letting tools move data between accounts or to AWS services without traffic ever leaving Amazon's backbone. or Azure Private Link directly from the Varonis integration wizard, with automatic endpoint URL generation, pre-deployment connectivity validation, and remediation guidance.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Private Cloud Data Collector secret management and Terraform deploymentnew62how completely this was documenteddepth22/40specificity25/30actionability15/3062 / 100
Private Cloud Data Collectors can now be configured to use AWS Secrets Manager, Azure Key Vault, or HashiCorp Vault as external secret stores for collector credential storage, and can also be deployed to AWS ECSAWS ECSAmazon's managed container orchestration service that runs Docker containers on clusters of EC2 instances or Fargate, letting tools offload scheduling, scaling, and infrastructure management to AWS. using Terraform for infrastructure-as-code management of collector environments.
Jira permissions visibility and overexposure detectionnew55how completely this was documenteddepth25/40specificity20/30actionability10/3055 / 100
Varonis tracks access to Jira content types — issues, comments, attachments, and worklogs — to surface who can access specific data and how that access is granted, and analyzes effective permissions across Jira to identify overexposed or broadly accessible resources.
GitHub Enterprise Cloud monitoring via GitHub Appnew50how completely this was documenteddepth20/40specificity20/30actionability10/3050 / 100
Adds GitHub Enterprise Cloud monitoring via a GitHub App integration, scoping permissions to only what is required for monitoring and classification activities while providing enterprise-wide coverage and flexible deployment options.
Customizable on-demand scan prioritizationnew42how completely this was documenteddepth20/40specificity10/30actionability12/3042 / 100
Adds on-demand scan prioritization, letting you select either a Prioritized Scan for immediate execution or a standard queued rescan, balancing urgency against resource efficiency.
Confluence page history scanning for sensitive datanew40how completely this was documenteddepth20/40specificity10/30actionability10/3040 / 100
Varonis now scans historical versions of Confluence pages to detect sensitive content, automatically tagging affected pages to support investigation and remediation workflows.
Varonis Private Cloud Data Collectors now support AWS Secrets Manager, Azure Key Vault, and HashiCorp Vault for credential storage.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Varonis adds flexible on-demand scan prioritization, letting you choose between a Prioritized Scan and a standard queued rescan.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Varonis now scans Confluence page history to surface sensitive data in older revisions and tag them for investigation.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Enables analysis of historical versions of Confluence pages to detect sensitive content, with automatic tagging of affected pages to support investigation and remediation workflows.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Varonis Private Cloud Data Collector can now be deployed to AWS ECSAWS ECSAmazon's managed container orchestration service that runs Docker containers on clusters of EC2 instances or Fargate, letting tools offload scheduling, scaling, and infrastructure management to AWS. using TerraformTerraformAn open-source infrastructure-as-code tool by HashiCorp that provisions cloud and on-premises resources through declarative configuration files, letting cyber tools automate and version-control their deployment environments..︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Varonis adds Jira content visibility — track and analyze permissions on issues, comments, attachments, and worklogs.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Tracks access to Jira content types — issues, comments, attachments, and worklogs — to surface who can access specific data and how that access is granted.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Analyzes effective permissions across Jira to identify overexposed or broadly accessible resources.
Varonis can now monitor GitHub Enterprise Cloud via a GitHub App with least-privilege permissions and enterprise-wide coverage.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Varonis now supports self-service Snowflake PrivateLinkPrivateLinkAn AWS networking feature that exposes a service over a private endpoint inside a VPC, so traffic never traverses the public internet, giving cyber tools a way to integrate with cloud services without opening public routes. configuration via the integration wizard for AWS and Azure.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Bold Security runs a local AI agent on every endpoint that blocks insider threats, data leakage and shadow-AI use.
Bold Security shipped a Wiz integration that feeds cloud resource exposure context into its endpoint agent's data-movement enforcement decisions.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
1 FEATURE0 OF 1 FEATUREmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Wiz integration for cloud-aware endpoint enforcementnew62how completely this was documenteddepth30/40specificity22/30actionability10/3062 / 100
Bold syncs the Wiz cloud resource inventory — including repository, bucket, and database sensitivity and exposure levels — directly to the endpoint agent, and keeps this sync ongoing so allow/deny lists don't need to be maintained statically as cloud environments change.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enforcement decisions become exposure-aware, evaluating both the origin cloud resource and destination of a data transfer (e.g. distinguishing a move from an internal repo to an access-controlled bucket versus to a public S3 bucket), and enriched data lineage carries a file's source cloud resource (private repo, internal bucket, production database) as context from the moment data moves.
— Explains mechanism and scope well but no config/API names or UI path given.launch-20260902-0521ae1a
Bold Security integrates with Wiz to bring cloud resource exposure context into endpoint data-movement enforcement decisions.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Integrates with Wiz to sync cloud resource inventory — including repository, bucket, and database sensitivity and exposure levels — directly to the Bold endpoint agent, so enforcement decisions reflect current cloud posture.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds exposure-aware enforcement that evaluates both the origin cloud resource and the destination of a data transfer, distinguishing a move from an internal repo to an access-controlled bucket from the same move to a public S3 bucket.
Adds enriched data lineage so a file's source cloud resource (private repo, internal bucket, production database) is carried as context to the endpoint from the moment data moves.
Automatically syncs the Wiz cloud resource inventory on an ongoing basis, eliminating the need to maintain static allow/deny lists as cloud environments change.
ToolHive is an enterprise-grade platform for running and managing Model Context Protocol (MCP) servers.
ToolHive v0.51.0 adds SPIFFESPIFFEAn open standard, maintained by the CNCF, for assigning cryptographic identities to workloads in dynamic infrastructure so services can authenticate each other without passwords or static credentials.JWT-SVIDJWT-SVIDA SPIFFE Verifiable Identity Document encoded as a JSON Web Token, used to prove workload identity across trust boundaries where X.509 certificates are impractical, such as HTTP headers. authentication, letting MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. clients authenticate to MCP servers using workload identityworkload identityAn identity assigned to software, such as a service or container, rather than a person. It lets the workload authenticate and receive permissions without sharing a user's credentials..︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
1 FEATURE1 OF 1 FEATUREmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0101
SPIFFE JWT-SVID authentication for MCP clientsnew35how completely this was documenteddepth15/40specificity15/30actionability5/3035 / 100
ToolHive now authenticates MCP clients using SPIFFE JWTJWTAn open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object passed between parties. Cyber tools use it to verify identity and permissions without querying a central session store.-SVIDs, enabling workload identity-based access control for MCP servers.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
— Names the mechanism (SPIFFE JWT-SVID) but no config or command shownv0.51.0
ToolHive v0.51.0 adds SPIFFESPIFFEAn open standard, maintained by the CNCF, for assigning cryptographic identities to workloads in dynamic infrastructure so services can authenticate each other without passwords or static credentials.JWT-SVIDJWT-SVIDA SPIFFE Verifiable Identity Document encoded as a JSON Web Token, used to prove workload identity across trust boundaries where X.509 certificates are impractical, such as HTTP headers. authentication for MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. clients.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ GET THIS VERSION
$ git clone --branch v0.51.0 https://github.com/stacklok/toolhive.git
# already have the repo? check out this version:$ git checkout v0.51.0
Authenticates MCP clients using SPIFFE JWTJWTAn open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object passed between parties. Cyber tools use it to verify identity and permissions without querying a central session store.-SVIDs, enabling workload identityworkload identityAn identity assigned to software, such as a service or container, rather than a person. It lets the workload authenticate and receive permissions without sharing a user's credentials.-based access control for MCP servers.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Obsidian 1.14.2 adds a command to open files from outside the vault, deeper Kanban folder-grouping support, and always-on fuzzy matching for link suggestions, while moving font-size sync out of appearance.json.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
The free and flexible app for your private thoughts.
Obsidian 1.14.2 adds a command to open files from outside the vault, deeper Kanban folder-grouping support, and always-on fuzzy matching for link suggestions, while moving font-size sync out of appearance.json.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ WHAT SHIPPED ·
6 FEATURES0 OF 6 FEATURESmost completely described firstwhat's the number?
Each feature carries 0–100 for how completely the vendor documented
it — not how big or important the work is. A major capability
described in eight words scores low, and that is the finding.
depth0–40what it does and how it works or what changed
specificity0–30names real surfaces — APIs, flags, formats, limits, numbers
actionability0–30enough to go use it — a named endpoint, flag, or config key tops this; a UI path is a starting point
Code and config rank first by construction: a documented endpoint,
flag or config key scores at the top of specificity and actionability,
so it sorts above a feature described only in prose. Under
60 the notes go thin — everything below the “thinner
coverage” line is thinner documentation, not smaller work.
Hover any meter for that feature's three sub-scores.
0100
Open file from outside the vault commandnew70how completely this was documenteddepth20/40specificity25/30actionability25/3070 / 100
Adds the Open file from outside the vault... command to open any file on your computer in the current window (Desktop only).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Open a standalone Markdown report or log file that lives outside your vault for quick review without moving it.
📍Open the command palette, search for 'Open file from outside the vault...', then navigate to and select any file on your filesystem.
Always-on fuzzy matching for link suggestionsimproved65how completely this was documenteddepth30/40specificity25/30actionability10/3065 / 100
The editor link suggestions (e.g. [[) and the quick switcher now always use fuzzy matching regardless of vault size, removing the 10,000-file threshold that previously triggered a simplified algorithm.
Kanban folder-grouping and error handlingimproved60how completely this was documenteddepth25/40specificity20/30actionability15/3060 / 100
Kanban boards grouped by file.folder now let cards be moved between folder columns, and creating a note in a column places it in the corresponding folder. Also adds error feedback when moving a card fails, such as when the note has invalid properties or the target folder is missing.
Base font size no longer synced via Obsidian Syncbreaking60how completely this was documenteddepth25/40specificity25/30actionability10/3060 / 100
Base font size is no longer saved to appearance.json and is now stored in device local storage, so it no longer syncs across devices via Obsidian Sync.
Set Obsidian as default Markdown appnew55how completely this was documenteddepth20/40specificity20/30actionability15/3055 / 100
Obsidian now registers itself in the OS Open with menu and can be set as the default app for Markdown files (requires reinstalling the latest installer).
Base font size is removed from appearance.json and stored in device local storage — any synced font size preference via Obsidian Sync will no longer propagate across devices.
Obsidian 1.14.2 lets you open files from outside the vault and always uses fuzzy matching in large vaults.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
Open a standalone Markdown report or log file that lives outside your vault for quick review without moving it.
📍Open the command palette, search for 'Open file from outside the vault...', then navigate to and select any file on your filesystem.
Adds the Open file from outside the vault... command to open any file on your computer in the current window (Desktop only).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Obsidian now registers itself in the OS Open with menu and can be set as the default app for Markdown files (requires reinstalling the latest installer).
Kanban: Cards can now be moved between folder columns when grouped by file.folder.
Kanban: Creating a note in a column now places it in the corresponding folder when grouped by file.folder.
Base font size is no longer saved to appearance.json and is now stored in device local storage, so it no longer syncs across devices via Obsidian Sync.
+3 moreshow less
iOS 27: Adds support for the new extra large Quick Capture and View Note widgets.
The editor link suggestions (e.g. [[) and the quick switcher now always use fuzzy matching regardless of vault size, removing the 10,000-file threshold that previously triggered a simplified algorithm.
Kanban: Adds error feedback when moving a card fails, such as when the note has invalid properties or the target folder is missing.
Adds the Open file from outside the vault... command to open any file on your computer in the current window (Desktop only).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Obsidian now registers itself in the OS Open with menu and can be set as the default app for Markdown files (requires reinstalling the latest installer).
iOS 27: Adds support for the new extra large Quick Capture and View Note widgets.
5 more in Everything
└──▷ BREAKING ON UPGRADE
!Base font size is removed from appearance.json and stored in device local storage — any synced font size preference via Obsidian Sync will no longer propagate across devices.
 THE CYBER TOOLCHAIN