Anchore
Faster Answers, Fewer False Positives with Anchore Enterprise v6.3 (2026-10-27) commercialThe section your link pointed to isn't on Anchore's page any more, so we've brought you to the top.
anchorectl app add iot-gateway \
  --contact-name "Product Security Officer" \
  --contact-email psirt@example.com \
  --description "Industrial IoT gateway - product with digital elements"

anchorectl app version add 2.4.0 --app iot-gateway --status released --release-date 2026-06-15
anchorectl app version asset add container-image-remote registry.example.com/iot-gateway/web-console:2.4.0 \
  --app iot-gateway --version 2.4.0 --asset web-console --wait

anchorectl app version asset add sbom telemetry-module-1.8.0.cdx.json \
  --app iot-gateway --version 2.4.0 --asset telemetry-module -t device --wait

anchorectl app update iot-gateway --policy-id eu-cra-baseline
anchorectl app version policy status get 2.4.0 --app iot-gateway --fail-based-on-results
anchorectl app version vex add 2.4.0 --app iot-gateway \
  --vuln-id CVE-2022-22965 \
  --pkg-name spring-beans \
  --pkg-type java-archive \
  --pkg-version 5.3.17 \
  --status affected \
  --action-statement "Security update 2.4.1 ships the supplier's fixed component."

anchorectl app version export vdr 2.4.0 --app iot-gateway -f iot-gateway-2.4.0-vdr.cdx.json
anchorectl image check <image> --detail -f
helm upgrade my-inventory anchore/k8s-inventory --set 'k8sInventory.inventory_ingest_overwrite=true' --set 'k8sInventory.inventory_ttl_days=7'
anchorectl app add my-vm-fleet --contact-name "Platform Team"
anchorectl app version add 2026-06-01 --app my-vm-fleet
anchorectl app version asset add filesystem / \
  --app my-vm-fleet \
  --version 2026-06-01 \
  --asset web-server-vm \
  --type virtual_machine_disk \
  --wait
sudo qemu-nbd --read-only --connect=/dev/nbd0 disk.qcow2
sudo mount -o ro /dev/nbd0p1 /mnt/vm
anchorectl app version asset add filesystem /mnt/vm \
  --app my-vm-fleet \
  --version 2026-06-01 \
  --asset web-server-vm-image \
  --type virtual_machine_disk \
  --wait
GET /v2/images/{image_digest}/vuln/{vuln_type}
anchorectl image one-time-scan <pull string>
Summary
Anchore is a commercial container-security platform that generates and manages software bills of materials, scans container images, filesystems, and VM disks for vulnerabilities, and checks the results against compliance policy for frameworks like NIST and FedRAMPFedRAMPA US government program that standardizes cloud security authorization, letting vendors get a single assessment accepted across federal agencies instead of repeating the process for each one.. It runs as a self-hosted or managed enterprise deployment, driven through the anchorectl CLI or its API, with a runtime admission controller that can extend policy checks into live Kubernetes clusters; an MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. server also exposes its findings to AI agents directly. It is aimed at DevSecOps and compliance teams, particularly in regulated and government environments, who need proof of compliance tied to specific controls rather than a simple pass/fail. Its policy engine factors in CVSSCVSSCommon Vulnerability Scoring System, a method for describing a vulnerability's characteristics and severity. Its score is not the probability that attackers will exploit it., CISA KEVCISA KEVA catalog maintained by the US Cybersecurity and Infrastructure Security Agency listing vulnerabilities confirmed to be actively exploited in the wild, giving cyber tools a vetted, authoritative prioritization signal., EPSSEPSSExploit Prediction Scoring System, an estimate of the probability that a published vulnerability will be exploited in the next 30 days. It helps prioritize investigation and patching., and VEX status to cut false positives, and supports time-bound allowlisting for POA&M-style remediation tracking.
How Anchore helps
Which components in my container images have known vulnerabilities?
scans image layers and reports matched packages against vulnerability data, tied to the specific package and version that introduced the flaw
Which of my VM images or golden templates are shipping vulnerable packages before I clone them into a fleet?
mounts the disk image read-only and generates an SBOM from its filesystem without needing an agent installed, so the scan happens before the image is ever booted into a fleet
Can I trace a component across both my running containers and my VM fleet from one query?
records container images, VM filesystems, and imported third-party SBOMs as asset types under the same application version, so a single query spans all three
Does this SBOM I received from a vendor meet the minimum data my compliance program requires?
reads CycloneDX and SPDX SBOMs and checks for the NTIA minimum elements — supplier, component name, version, package identifier, dependency relationships, author, and timestamp
Would scanning this whole live filesystem pick up noise from the running kernel instead of real findings?
skips pseudo-filesystems like /proc and /sys by default on full-root scans, and can be pointed at narrower paths like /usr or /opt when only a faster, targeted read is needed
Can an automated agent pull risk and policy answers out of my scan data without me scripting the API myself?
exposes curated tools for triage, policy checks, and risk reporting, and falls back to generic API calls for anything else, handling pagination and large responses so the queries hold up at scale
Languages
Features
Built from Anchore's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- Anchore covers 3 of the 8 vulnerability assessment methods capabilities we track.
- Anchore covers 2 of the 5 supply chain security capabilities we track.
What Anchore offers you
- Command-line interface9
- REST API7
- JSON data export5
- CI/CD pipeline integration3
- Agent-based deployment2
- MCP server2
- Role-based access control2
- Administrative audit log1
- Agentless deployment1
- CSV data export1
- GraphQL API support1
- Import from a competing product1
- Kubernetes-native deployment1
- Offline mode1
- Outbound webhooks (the product notifies you)1
- SAML SSO1
- Scheduled jobs1
- Single sign-on1
- Ticketing integration1
No capabilities match.
Container image vulnerability scanning 8 features Vulnerability assessment methods since 2024
Product-level policy enforcement shipped Attaches a policy to a product release version and evaluates it in CI — blocking the build when any KEV-listed or otherwise non-compliant finding is present — so compliance is tracked at the product level rather than the scan level.
Shared capability: Container image vulnerability scanning
Also counts toward: Command-line interface
release 21 total
-
Adds
ANCHORECTL_FAIL_BASED_ON_RESULTS=trueenvironment variable so pipelines skip passing the flag on every job. Enforce FedRAMP 20x Class C Requirements at Build Time with Anchore Enterprise (2026-10-01) · Oct 2026 · source · release history -
Adds
--fail-based-on-resultsflag toanchorectl image checkto exit with code 1 on any STOP finding, breaking CI builds before images reach the registry.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enforce FedRAMP 20x Class C Requirements at Build Time with Anchore Enterprise (2026-10-01) · Oct 2026 · source · release history -
Supports
--detailoutput onanchorectl image checkto print WARN findings without failing the job. Enforce FedRAMP 20x Class C Requirements at Build Time with Anchore Enterprise (2026-10-01) · Oct 2026 · source · release history -
Adds
anchorectl app update --policy-idandanchorectl app version policy status get --fail-based-on-resultsto attach and evaluate a CRA-focused policy (blocking on any KEV-listed finding) at the product level in CI. What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source · release history -
Application vulnerability-packages trigger supports
anchore_scoreandanchore_score_comparisonparameters for policy rules. 6.2.0 · Sep 2026 · source · release history - Policy Support for VEX Annotations allows policies to factor in Vulnerability Exploitability eXchange (VEX) status Extending Supply Chain Security to AI Models with Anchore Enterprise v6.2 (2026-09-15) · Sep 2026 · source · release history
example
-
Set the fail flag once in CI environment variables so every job enforces FedRAMP 20x policy without per-command flags.
ANCHORECTL_FAIL_BASED_ON_RESULTS=trueEnforce FedRAMP 20x Class C Requirements at Build Time with Anchore Enterprise (2026-10-01) · Oct 2026 · source -
Fail a CI pipeline immediately when any FedRAMP 20x STOP finding is detected, while still printing WARN findings for tracking.
anchorectl image add ${IMAGE} --wait anchorectl image check ${IMAGE} --detail --fail-based-on-resultsEnforce FedRAMP 20x Class C Requirements at Build Time with Anchore Enterprise (2026-10-01) · Oct 2026 · source -
Attach a live container image and a supplier-delivered CycloneDX SBOM as assets to a release version, then enforce a KEV-blocking CRA policy in CI so the build fails if any exploited vulnerability is present.
anchorectl app version asset add container-image-remote registry.example.com/iot-gateway/web-console:2.4.0 \ --app iot-gateway --version 2.4.0 --asset web-console --wait anchorectl app version asset…What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source
Reporting service shipped Exposes full container image information via a flexible GraphQL interface with configurable filtered reports and time-range queries.
Shared capability: Container image vulnerability scanning
Also counts toward: CSV data export, GraphQL API support, JSON data export
release 14 total
-
/apps/{app_id}/versions/{version_id}/packages-searchAPI gainshas_vulnerabilitiesandseverityfilters. 6.2.0 · Sep 2026 · source · release history - Analysis failure reasons now returned in API responses for centralized, distributed, and one-time scans. 6.2.0 · Sep 2026 · source · release history
- Package filtering by Vulnerability Severity (Critical, High, Medium) within application versions Extending Supply Chain Security to AI Models with Anchore Enterprise v6.2 (2026-09-15) · Sep 2026 · source · release history
- Allows downloading documents produced by asynchronous jobs directly from the job interface 6.1.0 · Aug 2026 · source · release history
- Adds quick vulnerability search by ID without requiring an App Version context 6.1.0 · Aug 2026 · source · release history
-
Adds
services.reports.use_volumeconfiguration to direct the Report Service to use disk space instead of memory for report generation 5.2.0 · Aug 2026 · source · release history
AI model artifact scanning shipped Natively inspects container images for AI/ML model artifacts such as GGUF files and indexes them within the central SBOM catalog alongside traditional software components.
Shared capability: Container image vulnerability scanning
release
-
Discovered AI models (GGUF and Docker Models) are now reported as packages inside application versions, making them visible in the same inventory as other components.
 Faster Answers, Fewer False Positives with Anchore Enterprise v6.3 (2026-10-27) · Oct 2026
· source
· release history
-
AI models in GGUF format are cataloged as content; retrieved via
GET /images/{image_digest}/content/model. 6.2.0 · Sep 2026 · source · release history -
Natively inspects container images for AI/ML model artifacts, including
GGUFfiles and Docker Model structures, indexing them as packages in the central SBOM catalog alongside traditional software components.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Extending Supply Chain Security to AI Models with Anchore Enterprise v6.2 (2026-09-15) · Sep 2026 · source · release history - AI "Model" Artifact Detection natively inspects container images for GGUF files and Docker Model structures Extending Supply Chain Security to AI Models with Anchore Enterprise v6.2 (2026-09-15) · Sep 2026 · source · release history
- Incorporates third-party vulnerability data feeds from Risk Based Security (VulnDB) to enhance image scanning results 2.1.0 · Sep 2024 · source · release history
Local SBOM generation shipped Generates and outputs SBOMs locally during image scanning workflows to allow inspection of component inventories before pushing artifacts.
Shared capability: Container image vulnerability scanning
Also counts toward: Import from a competing product
release
- Local SBOM Generation enables file system scan output during image scanning workflows Extending Supply Chain Security to AI Models with Anchore Enterprise v6.2 (2026-09-15) · Sep 2026 · source · release history
- Supports local SBOM generation and output during image scanning workflows, enabling developers to inspect component inventories and compliance status before pushing artifacts to central registries. Extending Supply Chain Security to AI Models with Anchore Enterprise v6.2 (2026-09-15) · Sep 2026 · source · release history
- Handles RPM modularity consistently at the SBOM boundary during SPDX scans 6.1.0 · Aug 2026 · source · release history
- Policy gates using license fields (e.g., GPL-2.0) may need updates to match normalized SPDX names (e.g., GPL-2.0-only). 5.16.0 · Aug 2026 · source · release history
- Enables Container Image SBOM generation and import from AnchoreCTL without Syft, supporting secret scans and filesystem metadata analysis 4.7.0 · Sep 2024 · source · release history
Detailed policy failure reporting shipped Surfaces per-control failure details and specific NIST controls in build and CLI outputs to support ATO assessments.
Shared capability: Container image vulnerability scanning
Also counts toward: CI/CD pipeline integration, Command-line interface
release
-
Surfaces per-control failure detail via
anchorectl image check <image> --detail -f, returning the specific control and finding that failed rather than a pass/fail count, enabling assessors to trace results to a named requirement.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ FedRAMP & CMMC in 2026: what actually changed for your Authority to Operate (ATO) (2026-09-22) · Sep 2026 · source · release history - Sorts policy findings by rule name 6.1.0 · Aug 2026 · source · release history
example
-
Fail a CI/CD build immediately on any CISA KEV-listed vulnerability and get the specific NIST control and finding — not just a pass/fail — so the result is directly traceable for an ATO assessor.
anchorectl image check <image> --detail -fFedRAMP & CMMC in 2026: what actually changed for your Authority to Operate (ATO) (2026-09-22) · Sep 2026 · source
Stateless image scanning shipped Performs lightweight vulnerability and policy scans on container images without persisting the results to the database.
Shared capability: Container image vulnerability scanning
Also counts toward: Command-line interface, REST API
release
-
Adds AnchoreCTL command
anchorectl image one-time-scan <pull string>for stateless scans 5.19.0 · Aug 2026 · source · release history -
Adds one-time stateless image scanning capability via
POST /v2/scanAPI endpoint 5.19.0 · Aug 2026 · source · release history
example
-
Perform a lightweight vulnerability and policy scan without persisting the result in the database.
anchorectl image one-time-scan <pull string>5.19.0 · Aug 2026 · source
Custom base image override shipped Allows users to tag container images with a specific base image annotation to control vulnerability comparison logic.
Shared capability: Container image vulnerability scanning
release
-
Adds
anchore.user/marked_base_imageannotation to override the system-determined base image for vulnerability checks 5.7.0 · Aug 2026 · source · release history
Priority analysis queue shipped Configures a dedicated processing queue to accelerate the analysis of high-priority container images.
Shared capability: Container image vulnerability scanning
release
-
Adds priority analysis queue feature configurable via
services.catalog.analysis_queue_priorityHelm chart value 5.19.0 · Aug 2026 · source · release history
CycloneDX SBOM 4 features Supply chain security since 2024
SBOM import and export format support shipped Exposes the ability to download SBOM data in SPDX and CycloneDX formats alongside native JSON, and imports supplier-delivered SBOMs.
Shared capability: CycloneDX SBOM
Also counts toward: JSON data export, REST API
release 11 total
- Enables importing third-party vendor-provided SBOMs in CycloneDX and SPDX formats Operationalizing SBOMs to Boost Incident Response Velocity with Anchore Enterprise v6.1 (2026-08-20) · Aug 2026 · source · release history
- Imports CycloneDX 1.7 SBOM documents alongside previously supported formats 6.1.0 · Aug 2026 · source · release history
- SBOM ingestion supports Syft, CycloneDX, and SPDX formats (with SPDX 3.x upload/download supported; analysis not yet functional). 6.0.0 · Aug 2026 · source · release history
- Package License Names are normalized to the SPDX License List for newly analyzed images. 5.16.0 · Aug 2026 · source · release history
- Image Hints results are visible in downloaded SBOMs (Syft, SPDX, CycloneDX) for newly analyzed images. 5.16.0 · Aug 2026 · source · release history
- New Imported SBOMs tab in the UI allows uploading SPDX/CycloneDX SBOMs for inventory and vulnerability analysis 5.18.0 · Aug 2026 · source · release history
Vulnerability Disclosure Report (VDR) export shipped Generates a Vulnerability Disclosure Report bundling product identity, component inventory, and VEX analysis into a single CycloneDX document suitable for regulatory submissions such as ENISA SRP.
Shared capability: CycloneDX SBOM
Also counts toward: Command-line interface, JSON data export, REST API
release
-
Adds
anchorectl app version export vdrsubcommand (with-ffor output file) to generate a Vulnerability Disclosure Report bundling product identity, component inventory, and VEX analysis into a single CycloneDX document suitable for ENISA SRP submission. What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source · release history -
anchorectl app version export vdrexports a Vulnerability Disclosure Report in CycloneDX format What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source · release history - Exports support SBOM (SPDX/CycloneDX), VDR (CycloneDX JSON/VEX-aware), VEX document, and CSV formats for vulnerabilities/packages/policy. 6.0.0 · Aug 2026 · source · release history
-
New API endpoints for CycloneDX Vulnerability Disclosure Reports (VDR):
GET /v2/images/{image_digest}/vuln/{vuln_type}/cyclonedx-jsonandGET /v2/images/{image_digest}/vuln/{vuln_type}/cyclonedx-xml. 5.23.0 · Aug 2026 · source · release history - UI feature allows exporting vulnerability data in VDR (CycloneDX) and VEX formats via the new Export dialog. 5.23.0 · Aug 2026 · source · release history
example
-
When a KEV match triggers a
policy_status_changedalert, record a VEX assessment and export a Vulnerability Disclosure Report ready for ENISA SRP submission — all before the 24-hour CRA clock expires.anchorectl app version vex add 2.4.0 --app iot-gateway \ --vuln-id CVE-2022-22965 \ --pkg-name spring-beans \ --pkg-type java-archive \ --pkg-version 5.3.17 \ --status affected \ --action-statement…What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source -
Export the complete evidence bundle (VEX, components, identity) as a CycloneDX VDR for submission to ENISA.
anchorectl app version export vdr 2.4.0 --app iot-gateway -f iot-gateway-2.4.0-vdr.cdx.jsonWhat EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source
Runtime inventory integration shipped Attaches live container images and supplier-delivered SBOMs (CycloneDX or SPDX) as typed assets to a versioned product release for unified management.
Shared capability: CycloneDX SBOM
Also counts toward: Agent-based deployment, REST API
release
-
Adds
anchore-k8s-inventoryandanchore-ecs-inventoryas new Runtime Inventory Agents for accessing Kubernetes and ECS environments 4.7.0 · Sep 2024 · source · release history -
Adds
/enterprise/inventories DELETEendpoint to remove runtime inventory contexts no longer reported by KAI 4.6.0 · Sep 2024 · source · release history -
Adds global metrics
anchore_monitor_inventory_contexts_monitored_total, anchore_monitor_inventory_images_total (found), anchore_monitor_inventory_images_total (success), and anchore_monitor_inventory_images_total (fail) for runtime inventory monitoring 4.6.0 · Sep 2024 · source · release history -
Adds the
runtimeInventoryUnscannedImagesreport query to list runtime inventory images that have not been analyzed 4.3.0 · Sep 2024 · source · release history - Improves Inventory Watcher logging conciseness at info level 4.6.0 · Sep 2024 · source · release history
example
-
Configure the agent to overwrite existing image records and set a 7-day TTL for runtime data retention.
helm upgrade my-inventory anchore/k8s-inventory --set 'k8sInventory.inventory_ingest_overwrite=true' --set 'k8sInventory.inventory_ttl_days=7'Your Kubernetes cluster is running images your registry scan never checked (2026-09-01) · Sep 2026 · source
Heterogeneous asset attachment shipped Attaches live container images and supplier-delivered SBOMs (CycloneDX or SPDX) as typed assets to a versioned product release for unified management.
Shared capability: CycloneDX SBOM
Also counts toward: CI/CD pipeline integration, Command-line interface
release
- Evaluates third-party and imported SBOMs against KSI-SCR-MIT and VDR-CSO-AKE checks, not only SBOMs generated by Anchore Enterprise. Enforce FedRAMP 20x Class C Requirements at Build Time with Anchore Enterprise (2026-10-01) · Oct 2026 · source · release history
-
Adds
anchorectl app version asset add container-image-remoteandanchorectl app version asset add sbomsubcommands to attach heterogeneous assets — direct container images or supplier-delivered SBOMs — to a versioned product release. What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source · release history - The OpenStack Swift object store driver has been removed. 6.0.0 · Aug 2026 · source · release history
example
-
Attach a live container image and a supplier-delivered CycloneDX SBOM as assets to a release version, then enforce a KEV-blocking CRA policy in CI so the build fails if any exploited vulnerability is present.
anchorectl app version asset add container-image-remote registry.example.com/iot-gateway/web-console:2.4.0 \ --app iot-gateway --version 2.4.0 --asset web-console --wait anchorectl app version asset…What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source
Vulnerability database matching 3 features Vulnerability assessment methods since 2024
Vulnerability feed configuration shipped Incorporates third-party vulnerability data feeds from Risk Based Security (VulnDB) and enables vulnerability matching for specific OS packages.
Shared capability: Vulnerability database matching
Also counts toward: Scheduled jobs
release 13 total
-
Recognizes Hummingbird as a supported distribution in the
vulnerability.vulnerability_data_unavailabletrigger 6.1.0 · Aug 2026 · source · release history - Integrates Ubuntu 24.04 Feed Provider support for vulnerability detection. 5.5.0 · Aug 2026 · source · release history
-
Adds KEV and EPSS vulnerability data to the GET
/v2/sources/{source_id}/vulnendpoint response. 5.21.0 · Aug 2026 · source · release history -
Adds KEV and EPSS vulnerability data to the GET
/v2/images/{image_digest}/vulnendpoint response. 5.21.0 · Aug 2026 · source · release history - Adds vulnerability matching and policy evaluation support for SecureOS and Arch Linux. 5.26.0 · Aug 2026 · source · release history
- Adds vulnerability data source support for Fedora, including EPEL packages sourced from the Bodhi update system. 5.26.0 · Aug 2026 · source · release history
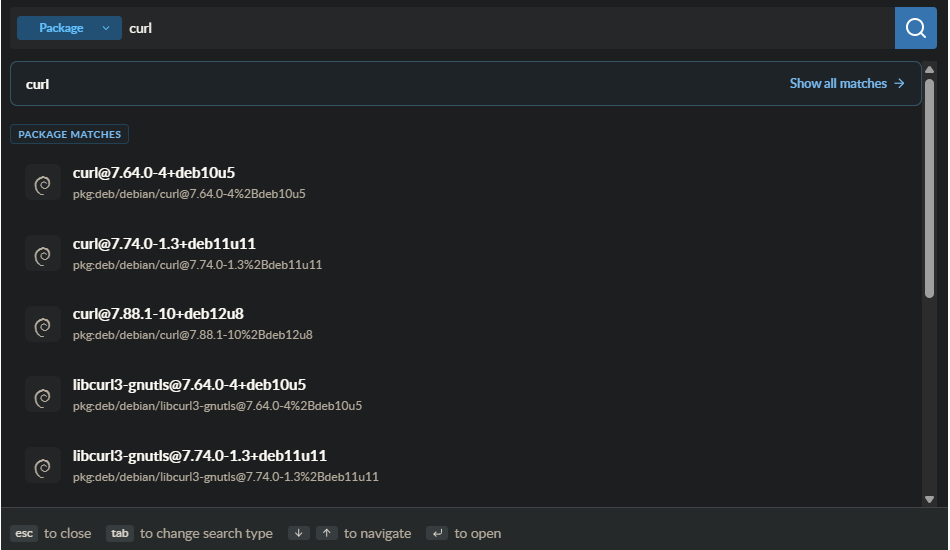
Quick Package Search shipped Searches for affected packages by name, name-plus-version, or PURL to identify exposure before a CVE is published or when no CVE is ever assigned.
Shared capability: Vulnerability database matching
release
-
Search for affected packages by name, name-plus-version, or PURL before a CVE is published — or when one never gets assigned — using the new Quick Package Search.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Faster Answers, Fewer False Positives with Anchore Enterprise v6.3 (2026-10-27) · Oct 2026
· source
· release history
Enhanced Go vulnerability matching shipped Improves Go vulnerability detection accuracy by using GoVulnDB symbols and configurable stdlib capture modes.
Shared capability: Vulnerability database matching
release
-
Go vulnerability matching now uses GoVulnDB symbols to reduce false positives; controlled by
golang.capture-symbolsconfig key (extended-stdlib,stdlib,all,none). 6.2.0 · Sep 2026 · source · release history
SBOM generation 2 features Supply chain security since 2024
Virtual machine SBOM generation shipped Generates Software Bill of Materials (SBOMs) from offline VM disk images or live virtual machine filesystems without requiring an agent, and attaches these assets to application versions for unified management.
Shared capability: SBOM generation
Also counts toward: Agentless deployment, Command-line interface, Offline mode
release
- Adds native filesystem scanning support for virtual machines alongside container images Operationalizing SBOMs to Boost Incident Response Velocity with Anchore Enterprise v6.1 (2026-08-20) · Aug 2026 · source · release history
-
Supports scanning VM disk images offline (read-only, no agent) via QEMU NBD mount —
sudo qemu-nbd --read-only --connect=/dev/nbd0 disk.qcow2— enabling forensic and golden-image workflows. What your SBOM inventory misses if it only covers containers (2026-08-18) · Aug 2026 · source · release history -
Unifies container images (
anchorectl app version asset add container-image), VM filesystems, and third-party SBOMs (anchorectl app version asset add sbom) as three asset types under one application version for cross-asset querying. What your SBOM inventory misses if it only covers containers (2026-08-18) · Aug 2026 · source · release history - Exposes the Anchore Enterprise V2 API as a consolidated endpoint for customers migrating from the distributed V1 APIs prior to v5.0.0 4.9.0 · Sep 2024 · source · release history
- Adds Single-Sign-On integration support for Okta, Keycloak, and Enterprise IDP systems via SAML/token-based authentication for API and client integrations 2.1.0 · Sep 2024 · source · release history
- API now supports querying a list of vulnerabilities found for a specific Application Version 4.3.0 · Sep 2024 · source · release history
example
-
Generate an SBOM from an offline VM disk image (read-only, no agent required) — useful for forensic analysis or scanning golden-image templates before fleet cloning.
sudo qemu-nbd --read-only --connect=/dev/nbd0 disk.qcow2 sudo mount -o ro /dev/nbd0p1 /mnt/vm anchorectl app version asset add filesystem /mnt/vm \ --app my-vm-fleet \ --version 2026-06-01 \ --asset…What your SBOM inventory misses if it only covers containers (2026-08-18) · Aug 2026 · source -
Scan a live VM's full filesystem and attach the resulting SBOM to an application version for unified querying alongside container assets.
anchorectl app add my-vm-fleet --contact-name "Platform Team" anchorectl app version add 2026-06-01 --app my-vm-fleet anchorectl app version asset add filesystem / \ --app my-vm-fleet \ --version…What your SBOM inventory misses if it only covers containers (2026-08-18) · Aug 2026 · source
Unified release SBOM export shipped Exports a single consolidated SBOM in CycloneDX or SPDX format covering all assets attached to a product release version.
Shared capability: SBOM generation
release
- Exports a unified SBOM per release version in CycloneDX and SPDX formats once all assets are attached. What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source · release history
- Enables download of SBOM data from the Artifact Analysis view in SPDX and OWASP CycloneDX formats alongside the native JSON format 4.5.0 · Sep 2024 · source · release history
-
Adds
licensesfield (array type) to API responses for content packages, supplementing the existing comma-delimitedlicensestring field 2.3.1 · Sep 2024 · source · release history
Vulnerability prioritization 1 feature Vulnerability assessment methods since 2026
Anchore Score risk weighting shipped Calculates a composite 0-100 risk score for vulnerabilities by blending CVSS, severity, EPSS, and KEV signals.
Shared capability: Vulnerability prioritization
release
-
Application vulnerability-packages trigger supports
anchore_scoreandanchore_score_comparisonparameters for policy rules. 6.2.0 · Sep 2026 · source · release history - New Anchore Score composite metric combines CVSS, EPSS, and CISA KEV for vulnerability prioritization 5.18.0 · Aug 2026 · source · release history
Other / not yet classified 22 features Features we have not matched to a capability yet. A suggested match is marked.
System monitoring and metrics shipped Adds global metrics for runtime inventory monitoring, analyzer status, and a System Dashboard to review deployment status.
release 16 total
-
Application log output can be set to JSON via
ANCHORE_LOG_FORMATenvironment variable. 6.2.0 · Sep 2026 · source · release history - Makes per-service resource limits configurable 6.1.0 · Aug 2026 · source · release history
- Captures database diagnostics in support bundles for faster troubleshooting 6.1.0 · Aug 2026 · source · release history
- Enables at-rest encryption for sensitive database columns with AES-256-GCM using a keyring defined in the config file 6.1.0 · Aug 2026 · source · release history
- Adds new Prometheus deployment metrics for monitoring Anchore Enterprise 5.19.0 · Aug 2026 · source · release history
-
Adds system statistic
stig_evaluation_inventoryto track STIG evaluation counts 5.19.0 · Aug 2026 · source · release history
Policy compliance alerting shipped Triggers automated notifications when policy outcomes change at the application version level to alert security teams of non-compliance.
Also counts toward: Ticketing integration, Outbound webhooks (the product notifies you)
release 11 total
-
Anchore Enterprise now fires detailed notifications when a known vulnerability's CVSS score or severity, EPSS score, or CISA KEV status changes after initial triage.
Faster Answers, Fewer False Positives with Anchore Enterprise v6.3 (2026-10-27) · Oct 2026
· source
· release history
-
Supports continuous post-ship monitoring via
vuln_update,policy_eval, andalertssubscriptions that surface new KEV matches and Pass-to-Fail flips without a rebuild. Enforce FedRAMP 20x Class C Requirements at Build Time with Anchore Enterprise (2026-10-01) · Oct 2026 · source · release history - Continuously re-evaluates every stored SBOM against updated vulnerability data and policy automatically — flagging a newly non-compliant release the moment underlying data changes, not at the next scheduled scan. What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source · release history
-
Emits
policy_status_changednotifications at the Application Version level whenever a release's compliance outcome shifts, with subscription endpoints including Webhooks, Slack, Teams, Jira, GitHub, and email. What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source · release history -
Automated
policy_status_changednotifications for compliance shifts What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source · release history - Events raised when Application Version policy outcome changes (pass/warn/fail transitions). 6.2.0 · Sep 2026 · source · release history
Product-level release modeling shipped suggested Models a software product as an App with discrete versioned releases so that scans, policy evaluations, SBOM exports, and VDR generation are scoped to a named product release rather than individual ad-hoc image scans.
Suggested capability: Container image vulnerability scanning. This is our guess, not confirmed.
Also counts toward: Command-line interface
release 10 total
-
Adds
anchorectl app addandanchorectl app version addsubcommands to model a product as an App and each release as a Version, enabling product-level (not scan-level) compliance tracking.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source · release history - Expands the unified asset model to support global compliance regulations including EU CRA Operationalizing SBOMs to Boost Incident Response Velocity with Anchore Enterprise v6.1 (2026-08-20) · Aug 2026 · source · release history
- Apps model organizes software under App Versions which roll up Assets (container images/SBOMs) for aggregated SBOM content, vulnerability findings, and policy compliance results. 6.0.0 · Aug 2026 · source · release history
- Public APIs expose the new Apps API for managing Apps, Versions, and Assets via standard endpoints. 6.0.0 · Aug 2026 · source · release history
- Introduces a new Vulnerabilities by Kubernetes Namespace report template to filter findings by namespace 4.7.0 · Sep 2024 · source · release history
- Adds configurable filtered reports (tabular HTML, JSON, or CSV) for image, security, and policy status in the GUI Reports control 2.1.0 · Sep 2024 · source · release history
example
-
Model a product and released version in Anchore Enterprise so every subsequent scan, policy evaluation, and VDR export is scoped to that release rather than an ad-hoc image scan.
anchorectl app add iot-gateway \ --contact-name "Product Security Officer" \ --contact-email psirt@example.com \ --description "Industrial IoT gateway - product with digital elements" anchorectl app…What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source
Identity management integration shipped Adds LDAP/AD identity management integration and SSO support for Okta, Keycloak, and Enterprise IDP systems.
Also counts toward: Role-based access control, Single sign-on, SAML SSO
release 8 total
-
Adds
account-viewersystem role for listing all accounts within Anchore Enterprise 5.2.0 · Aug 2026 · source · release history -
Adds the
system-adminRBAC role to grant administrative privileges to non-admin account members. 5.11.0 · Aug 2026 · source · release history - Allows admin users to create API Keys for managing Accounts, User Groups, and RBAC Roles 5.7.0 · Aug 2026 · source · release history
-
Enables SSO-only mode (disabling local login) via
sso_auth_onlyconfiguration option 5.7.0 · Aug 2026 · source · release history - Adds a new user-viewer role assignable to groups or users for viewing all users across accounts via AnchoreCTL or API. 5.26.0 · Aug 2026 · source · release history
- API Keys are now supported for authentication with Anchore Enterprise, generated via the System > Accounts view in the UI or the new endpoint. 5.1.0 · Aug 2026 · source · release history
VEX assessment recording shipped Records engineering VEX annotations (status and action statement) against specific vulnerabilities and packages within a named product release version.
Also counts toward: Command-line interface, JSON data export, REST API
release
-
anchorectl app version vex addallows adding VEX annotations to a release version What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source · release history -
Adds
anchorectl app version vex addsubcommand with--vuln-id,--pkg-name,--pkg-type,--pkg-version,--status, and--action-statementflags to record engineering VEX annotations against a specific release. What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source · release history -
Adds VEX document generation via the
GET /v2/images/{image_digest}/vex/openvexAPI endpoint 5.22.0 · Nov 2025 · source · release history -
Adds new
vuln-annotator-editorRBAC role for creating and modifying vulnerability annotations 5.22.0 · Nov 2025 · source · release history
example
-
When a KEV match triggers a
policy_status_changedalert, record a VEX assessment and export a Vulnerability Disclosure Report ready for ENISA SRP submission — all before the 24-hour CRA clock expires.anchorectl app version vex add 2.4.0 --app iot-gateway \ --vuln-id CVE-2022-22965 \ --pkg-name spring-beans \ --pkg-type java-archive \ --pkg-version 5.3.17 \ --status affected \ --action-statement…What EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source
Role-based access control shipped Provides a dedicated RBAC role for creating and modifying vulnerability annotations.
previously: RBAC for vulnerability annotations
Also counts toward: Role-based access control
release
-
New
application-editorandapplication-deleteRBAC roles manage access to the Apps model hierarchy. 6.0.0 · Aug 2026 · source · release history -
Adds a
user-viewerrole in the system domain providing read-only access to user-related information 5.25.0 · Aug 2026 · source · release history -
Adds
image-developerRBAC role to limit users to viewing images, vulnerabilities, policies and policy evaluations 5.0.0 · Aug 2026 · source · release history -
Adds
image-deleteRBAC role to allow users to delete images, sources, and archives from the system 5.12.0 · Aug 2026 · source · release history -
Adds new
vuln-annotator-editorRBAC role for creating and modifying vulnerability annotations 5.22.0 · Nov 2025 · source · release history
Failed image lifecycle management shipped suggested Provides policies to identify and automatically delete container images that remain in a failed analysis state.
Suggested capability: Container image vulnerability scanning. This is our guess, not confirmed.
release
- Improves garbage collection for deleted objects, jobs, and component catalog 6.1.0 · Aug 2026 · source · release history
- Adds support for selecting images that are in a failed analysis state for deletion via Artifact Lifecycle Policies. 5.21.0 · Aug 2026 · source · release history
- Adds Artifact Lifecycle Policy support for Imported SBOMs to enable automatic deletion based on user-defined criteria 5.25.0 · Aug 2026 · source · release history
- Artifact Lifecycle Policies now support a new condition to preserve base images from removal during retention enforcement. 5.6.0 · Aug 2026 · source · release history
Kubernetes STIG evaluation shipped Runs Security Technical Implementation Guide assessments against container workloads running in Kubernetes clusters.
Also counts toward: REST API
release
- Enables STIG Evaluations on Kubernetes Containers. 5.21.0 · Aug 2026 · source · release history
-
Adds support for STIG evaluations via
Static STIG AddOnentitlement 5.19.0 · Aug 2026 · source · release history -
New API endpoint for STIG profiles:
GET /v2/stig-profiles. 5.23.0 · Aug 2026 · source · release history -
Adds
policy gate stigto enforce STIG compliance in policy bundles 5.19.0 · Aug 2026 · source · release history
Compliance policy packs shipped Provides a built-in FedRAMP 20x Class C policy pack that maps Key Security Indicators and VDR requirements to automated image and SBOM checks with STOP/WARN/GO enforcement actions.
previously: FedRAMP 20x policy pack
release
- Ships a built-in allowlist tied to VER-AGM-MAP so every accepted risk carries an expiration date aligned to the POA&M. Enforce FedRAMP 20x Class C Requirements at Build Time with Anchore Enterprise (2026-10-01) · Oct 2026 · source · release history
- Introduces a FedRAMP 20x Class C policy pack that maps 11 KSIs and VDR requirements to 23 automated image checks and 4 SBOM checks, with STOP/WARN/GO actions per rule. Enforce FedRAMP 20x Class C Requirements at Build Time with Anchore Enterprise (2026-10-01) · Oct 2026 · source · release history
- Bundles ASD8, PCI-DSS, and CMMC compliance policy packs in addition to refreshed existing packs 6.1.0 · Aug 2026 · source · release history
Anchore Enterprise MCP Server shipped Provides a Model Context Protocol server for AI agents to query vulnerability findings, policy results, and SBOM data.
Also counts toward: MCP server
release
- New Anchore Enterprise MCP Server provides structured access to vulnerability findings, policy results, and SBOM data for AI agents Extending Supply Chain Security to AI Models with Anchore Enterprise v6.2 (2026-09-15) · Sep 2026 · source · release history
- Provides the Anchore Enterprise MCP server to expose security data and signals directly to AI agents Anchore + AI Just Got Easier: The Anchore Enterprise MCP Server (2026-09-03) · Sep 2026 · source · release history
example
-
Configure a policy to stop on any Known Exploited Vulnerability (KEV) finding for the eu-cra-baseline standard.
anchorectl app update iot-gateway --policy-id eu-cra-baselineWhat EU CRA’s 24-hour deadline means for your SBOM (2026-09-29) · Sep 2026 · source
Stale vulnerability feed detection shipped Fails policy evaluations when vulnerability feed data has not synced within a configurable window, preventing silent monitoring gaps from stale data.
release
- Adds a stale-feed rule that fails evaluations when vulnerability data has not synced in 15 days, preventing silent monitoring gaps. Enforce FedRAMP 20x Class C Requirements at Build Time with Anchore Enterprise (2026-10-01) · Oct 2026 · source · release history
- Policy Evaluation Policy now supports evaluating imported SBOM artifacts against policies with package, denylist, and stale feed data triggers 5.24.0 · Aug 2026 · source · release history
Kubernetes runtime enforcement shipped Extends policy enforcement to live Kubernetes clusters via an admission controller that blocks non-compliant workloads before scheduling.
release
- Extends policy enforcement from build time into live Kubernetes clusters via a runtime inventory and admission controller that blocks non-compliant workloads before scheduling. FedRAMP & CMMC in 2026: what actually changed for your Authority to Operate (ATO) (2026-09-22) · Sep 2026 · source · release history
- Enables policy evaluation and blocking against live runtime images via Kubernetes Admission Controller when configured. Your Kubernetes cluster is running images your registry scan never checked (2026-09-01) · Sep 2026 · source · release history
POA&M remediation tracking shipped Supports Plans of Action and Milestones by allowing time-bound allowlists for non-compliant findings with explicit remediation dates.
release
- Supports POA&M enforcement through policies, gates, and time-bound allowlists, letting a non-compliant finding be allowlisted with an explicit remediation date rather than silently ignored or blocking all builds. FedRAMP & CMMC in 2026: what actually changed for your Authority to Operate (ATO) (2026-09-22) · Sep 2026 · source · release history
- Adds POA&M-as-code capability allowing management of allowlists and remediation plans within security workflows Operationalizing SBOMs to Boost Incident Response Velocity with Anchore Enterprise v6.1 (2026-08-20) · Aug 2026 · source · release history
Scalable agentic API access shipped Provides a lightweight container image exposing curated tools for AI agents to query vulnerability findings, policy results, and SBOM data at scale with automatic pagination and response handling.
Also counts toward: MCP server
release
- Handles large payload management, pagination, and consistent response handling automatically within the MCP server, enabling agentic workflows to query Anchore at scale. Anchore + AI Just Got Easier: The Anchore Enterprise MCP Server (2026-09-03) · Sep 2026 · source · release history
- Exposes curated MCP tools covering key API properties for specific security objectives (triage, policy checks, risk reporting), with a fallback to generic API invocation for broader coverage. Anchore + AI Just Got Easier: The Anchore Enterprise MCP Server (2026-09-03) · Sep 2026 · source · release history
Kubernetes inventory agent shipped Provides a Helm-installable agent that polls the K8s API to populate runtime inventory data.
Also counts toward: Agent-based deployment, Command-line interface, Kubernetes-native deployment
release
-
Adds
helm install anchore/k8s-inventorysubpackage for the new Kubernetes inventory agent that polls the K8s API directly. Your Kubernetes cluster is running images your registry scan never checked (2026-09-01) · Sep 2026 · source · release history - New AnchoreCTL commands to view integration health status for k8s-inventory agents. 5.11.0 · Aug 2026 · source · release history
Configurable malware scanning shipped Enables custom timeout thresholds and supports splitting large images to ensure reliable ClamAV analysis.
Also counts toward: REST API
release
-
New
max_scan_timeconfiguration option exposed via API and UI to control ClamAV malware scan timeout in milliseconds 5.18.0 · Aug 2026 · source · release history - Adds support for Malware Scanning on images larger than 4 GB by splitting them into 2 GB chunks during analysis 5.13.0 · Aug 2026 · source · release history
VEX document generation shipped suggested Generates VEX documents via an API endpoint.
Suggested capability: Container image vulnerability scanning. This is our guess, not confirmed.
Also counts toward: JSON data export
release
-
New API endpoint for CycloneDX Vulnerability Exploitability eXchange (VEX) documents:
GET /v2/images/{image_digest}/vex/cyclonedx-jsonandGET /v2/images/{image_digest}/vex/cyclonedx-xml. 5.23.0 · Aug 2026 · source · release history -
Adds VEX document generation via the
GET /v2/images/{image_digest}/vex/openvexAPI endpoint 5.22.0 · Nov 2025 · source · release history
Artifact registry integration shipped suggested Adds full support for CNCF Harbor project as an integrated artifact registry.
Suggested capability: Container image vulnerability scanning. This is our guess, not confirmed.
release
- Adds PURL support in Artifact Analysis UI with a dedicated column in the Contents table 5.22.0 · Nov 2025 · source · release history
- Adds full support for CNCF Harbor project v1.10++ as an integrated artifact registry. 2.2.0 · Sep 2024 · source · release history
AI model pipeline policy gating shipped Evaluates AI model artifacts in CI pipelines using the packages policy gate, enforcing Fail (hard stop) or Warn (flag for review) outcomes.
Also counts toward: CI/CD pipeline integration
release
-
Gate AI models in pipeline policy with two outcomes — Fail (hard stop) or Warn (flag for parallel vetting) — using the new packages policy gate for AI models.
Faster Answers, Fewer False Positives with Anchore Enterprise v6.3 (2026-10-27) · Oct 2026
· source
· release history
License management shipped Manages software licenses and supports adding free-text comments during license creation and updates.
release
- Accepts free-text comments on license create, update, and retrieval operations 6.1.0 · Aug 2026 · source · release history
API audit logging shipped Captures and records access events for designated API service endpoints to track administrative and user actions.
Also counts toward: Administrative audit log
release
-
Adds
AUDITevent logging for specified API endpoints in the API Service 5.4.0 · Aug 2026 · source · release history
Policy hub integration shipped Enables viewing, listing, and importing pre-made policies from the Anchore Policy Hub via the Policy Hub GUI.
release
- Enables viewing, listing, and importing pre-made policies from the Anchore Policy Hub via the Policy Hub GUI 2.1.0 · Sep 2024 · source · release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
4 commands for Anchore, each with where it came from. This tool has no source analysis yet, so there is no option reference and no captured run beside them.
No command matches.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for Anchore, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Anchore puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Website history
anchore.com, every changeAnchore's home, pricing and product pages and 24 more pages as they looked each month from September 2021 to October 2026: 64 renders, 7 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Coverage
Missing something? Tell us
What Anchore connects to, runs on and detects, read from its release notes and docs. So far: 1 new supported platform.
1 change, tracked since Oct 27, 2026.
-
Oct 272026
new Ubuntu ESM vulnerability data feed support
Anchore Enterprise v6.3 eliminates false positives on Ubuntu ESM images. It recognizes ESM images and evaluates them against a separate vulnerability data feed that covers ESM fixes, so findings reflect what is actually patched. This builds on the existing Red Hat Extended Update Support (EUS) to cover the Ubuntu ecosystem.
Operating systems 1
Nothing first seen in this window. That doesn't mean Anchore shipped nothing, only that we found no record of it.
How we count
Read from 1 of 58 release notes and docs updates we hold for Anchore. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through Anchore's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
58 entries
No entries match these filters.
- October 20261
- September 20266
- August 202632
- June 20261
- December 20251
- November 20251
- September 202416
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →