Artemis Security
commercialThe section your link pointed to isn't on Artemis Security's page any more, so we've brought you to the top.
Artemis Security is a cybersecurity platform that provides detection, investigation, threat hunting, and response using a unified model of a customer's environment.
Summary
Artemis Security is a commercial SIEMSIEMSecurity information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents. that provides an AI-native Protection Platform aimed at reducing Mean Time to Detect and Mean Time to Respond against modern threats. It operates as a service and is built for security teams dealing with contemporary threat landscapes. Its documentation positions it as an alternative to traditional SIEMsSIEMsSecurity Information and Event Management platforms that collect, normalize, and correlate log data across an infrastructure so cyber tools can detect threats and trigger alerts from a central point., and the platform has seen three releases within the tracked window.
Artemis Security is a cybersecurity platform that provides detection, investigation, threat hunting, and response using a unified model of a customer's environment.
How Artemis Security helps
Which alerts in our queue actually warrant an analyst's attention right now?
scores and prioritizes incoming detections against current threat context, surfacing the ones most likely to be real incidents rather than noise
Which of the threats hitting us today would our old detection rules have missed?
applies AI-native detection logic tuned to current attack patterns rather than static signatures, catching activity that predates those patterns
Is a slow investigation on our side or a slow response from the platform?
separates detection time from response time across an incident so the bottleneck can be pinned to triage, escalation, or containment
Where in our environment is a threat actor moving right now?
correlates related detections across hosts, accounts, and services into a single incident timeline instead of leaving them as isolated alerts
Are we spending analyst time on the same false positives every week?
groups recurring low-value detections by pattern so the noisy sources can be identified and tuned down at the source
Languages
Features
Built from Artemis Security's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- Artemis Security covers 1 of the 2 detection engineering capabilities we track.
- Artemis Security covers 1 of the 11 logs and telemetry capabilities we track.
What Artemis Security offers you
- Administrative audit log1
No capabilities match.
All capabilities 3 capabilities
Cursor Origin repository access shipped Grants Artemis read-only access to Cursor Origin repositories — including contents, metadata, pull requests, reviews, checks, and rulesets — to provide context for AI-driven investigations.
release
- Supports GitHub (including GitHub Enterprise Server), GitLab, Bitbucket Cloud, and Cursor Origin as detection repository hosts. announced · Oct 2026 · source · release history
- Launches as a native integration with Cursor Origin marketplace from day one, authorized via the Artemis app for Origin with admin-approved write access. announced · Oct 2026 · source · release history
-
Makes the Artemis app available under the Security Category in Origin's app settings, creating the Origin connector in one step.
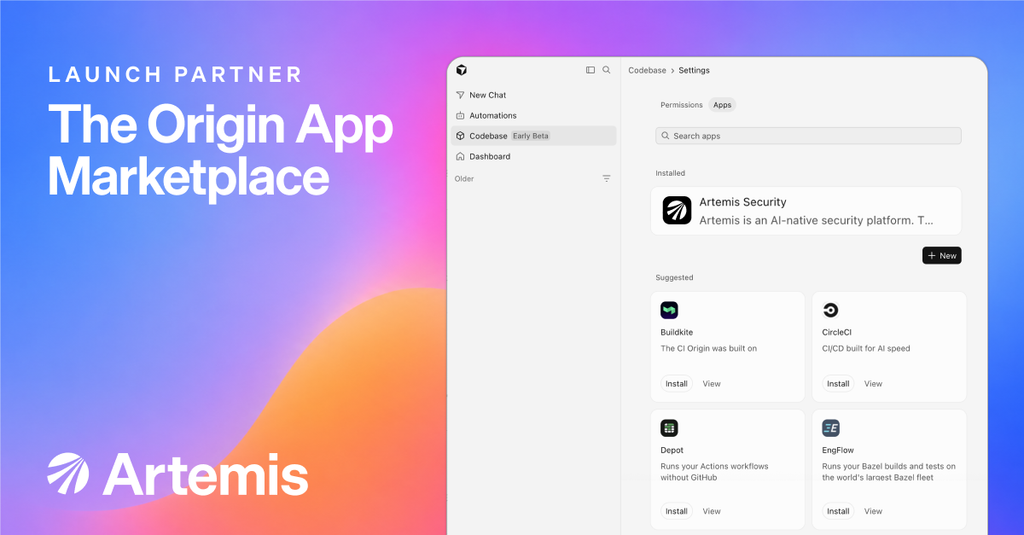 announced · Oct 2026
· source
· release history
- Adds an Artemis app for Cursor Origin that grants read-only access to customer repositories — contents, metadata, pull requests, reviews, checks, and rulesets — for AI-driven investigation context. announced · Oct 2026 · source · release history
- Installs the Origin connector directly from the Artemis portal via Install on Origin on the connector's setup page, with no new account or personal access token required. announced · Oct 2026 · source · release history
example
-
Install the Artemis app from Cursor Origin to enable read-only code access for AI-driven security investigations.
In Origin, go to app settings > Security Category, find the Artemis app, and install it. The installer redirects to the Artemis portal and creates the Origin connector automatically.announced · Oct 2026 · source
Detection as Code shipped Connects a repository so Artemis manages detections as pull requests — pushing new and tuned detections with explanations, organizing existing detections by data source on first connect, and picking up engineer edits merged through the standard pull request flow.
Shared capability: Detection as code
release
- Respects existing branch protection rules and required checks; detections stay unchanged until a pull request merges. announced · Oct 2026 · source · release history
- Pushes every new or tuned detection — adaptive, intelligence, user-created, and AI Mode detectors — to your repository as a pull request with an explanation and a link back to the detection in Artemis. announced · Oct 2026 · source · release history
- Enables Detection as Code via Settings → Detectors → Detection as Code to connect a repository and manage detections as pull requests.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Oct 2026 · source · release history
- Allows engineers to edit detections in their own editor and merge via the standard pull request flow; Artemis picks up the change automatically. announced · Oct 2026 · source · release history
- Organizes your existing detections by data source in the first pull request Artemis opens when a repository is connected. announced · Oct 2026 · source · release history
example
-
Connect a GitHub repository so Artemis opens pull requests for every new or tuned detection your organization owns.
In the Artemis portal, go to Settings → Detectors → Detection as Code, select your repository host (e.g. GitHub), choose a repository and branch, and click Connect.announced · Oct 2026 · source
Cursor Audit Logs ingestion shipped Ingests Cursor audit log events — including logins, member and role changes, API key and token activity, team and privacy settings, and Origin namespace, repository, and app-installation events — to detect suspicious activity.
Shared capability: Log collection
Also counts toward: Administrative audit log
release
-
Adds a Cursor Audit Logs connector that ingests logins, member and role changes, API key and token activity, team and privacy settings, and Origin namespace, repository, and app-installation events.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
announced · Oct 2026
· source
· release history
example
-
Connect Cursor Audit Logs to Artemis to start detecting suspicious logins, role changes, and token activity across your Origin environment.
In the Artemis portal, go to the connector setup page for 'Cursor Audit Logs' and click 'Install on Origin'.announced · Oct 2026 · source
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for Artemis Security, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Artemis Security puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Website history
artemissecurity.com, every changeArtemis's home and product pages and 18 more pages as they looked each month from March 2026 to October 2026: 32 renders, 4 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Releases
2 entries
No entries match these filters.
- October 20262
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →