Joe Security (Joe Sandbox)
The Sandbox That Fights Back: Introducing Adaptive Detonation (2026-11-03) commercialThe section your link pointed to isn't on Joe Security (Joe Sandbox)'s page any more, so we've brought you to the top.
Joe Sandbox is a malware analysis platform by Joe Security that performs deep malware and phishing analysis, including endpoint detection and behavior inspection.
Summary
Joe Security (Joe Sandbox) is a commercial malware-analysis platform that detonates suspicious files and URLs in instrumented environments to expose their behavior. It runs as a service, reachable through commands to submit a file, check whether the server is online, and pull back results by submission ID, which fits into an automated analysis pipeline rather than sitting on an analyst's laptop. It is built for SOCSOCA security operations center, the team or function that monitors threats, investigates alerts and coordinates incident response. Its work can be internal, outsourced or shared. analysts and malware researchers who need IOCIOCAn indicator of compromise, an observable clue that may point to malicious activity, such as a suspicious file hash or domain. It is evidence to investigate, rather than proof by itself. extraction and family classification without manual reverse engineering, backed by custom YARA and Suricata rule sets, behavior signatures, and configuration extractors updated for current families. Its Joe Reverser component adds an agentic analyst that investigates phishing, malicious documents, and web-based threats autonomously, while DOMDOMThe browser's in-memory tree representation of a web page's structure, standardized by the W3C, giving cyber tools a programmable interface to read or manipulate page content at runtime. extraction, QR-code decoding, and anti-evasion protections handle harder detection cases. Launched in 2011 and still shipping releases weekly, it is an actively maintained project.
Joe Sandbox is a malware analysis platform by Joe Security that performs deep malware and phishing analysis, including endpoint detection and behavior inspection.
How Joe Security (Joe Sandbox) helps
Is this file safe to let onto the network, or does it behave like malware once it runs?
detonates the file in an instrumented sandbox and reports the behaviors it triggered, matched against behavior signatures and custom YARA rules for known ransomware, stealer, RAT, and phishing families
What is this malware family, and what are its command-and-control details?
runs the sample through configuration extractors that pull IOCs and family-specific configuration data directly from memory or disk artifacts, without an analyst reverse engineering it by hand
Does this phishing page or document actually lead somewhere malicious?
extracts the page's DOM and any QR codes to follow obfuscated scripts, redirect chains, and embedded URLs that a static look at the file would miss
Would this sample behave differently if it knew it was being watched?
runs it under evasion-resistant conditions, including protection against macOS shutdown tricks and detection of VM/analysis-aware behavior, so the reported behavior matches what happens on a real victim machine
Which network signatures would this traffic have tripped on a real IDS?
runs captured traffic against Suricata rules covering malware, phishing, and anomaly categories, so the result names the concrete rule that would have fired
Can an analyst step in and steer the detonation while it's running?
supports live interaction with the analysis machine during the run, letting an analyst manually click through or redirect the sample's execution instead of only reading the report afterward
Languages
Features
Built from Joe Security (Joe Sandbox)'s releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- Joe Security (Joe Sandbox) covers 2 of the 8 investigation and response capabilities we track.
What Joe Security (Joe Sandbox) offers you
- SIEM forwarding2
- REST API1
No capabilities match.
Malware sandbox analysis 4 features Investigation and response since 2026
File submission for analysis shipped Submit a local file to Joe Sandbox and receive a submission ID for tracking the analysis.
Shared capability: Malware sandbox analysis
Also counts toward: REST API
release 9 total
- Adds RESTful Web API for submitting samples to Joe Reverser for fully automated background analysis without interactive chat Joe Reverser 2.1 Golden Eagle (2026-09-14) · Sep 2026 · source · release history
- Enhances the browser agent with VPN and proxy support to reduce bot-detection interference and improve stealth during phishing investigations Joe Reverser 2.1 Golden Eagle (2026-09-14) · Sep 2026 · source · release history
-
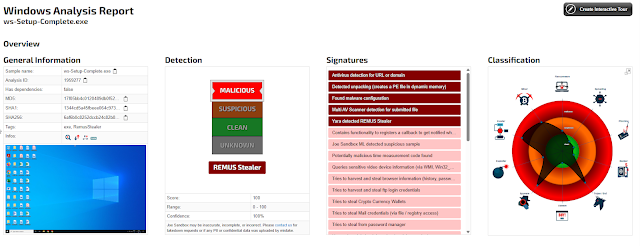
Improves prevention of VM and analysis system detection techniques used by evasive malware.
 Joe Sandbox v45 - Green Opal (2026-09-07) · Sep 2026
· source
· release history
- Updates the underlying Suricata engine to Suricata 8. Joe Sandbox v45 - Green Opal (2026-09-07) · Sep 2026 · source · release history
- Improves Live Interaction responsiveness and performance for smoother manual analyst interaction with analysis machines. Joe Sandbox v45 - Green Opal (2026-09-07) · Sep 2026 · source · release history
- Adds macOS shutdown protection to prevent analysis evasion via system shutdown on macOS samples. Joe Sandbox v45 - Green Opal (2026-09-07) · Sep 2026 · source · release history
example
-
Submit a local file for analysis; returns a submission_id.
jbxapi submit sample.docx
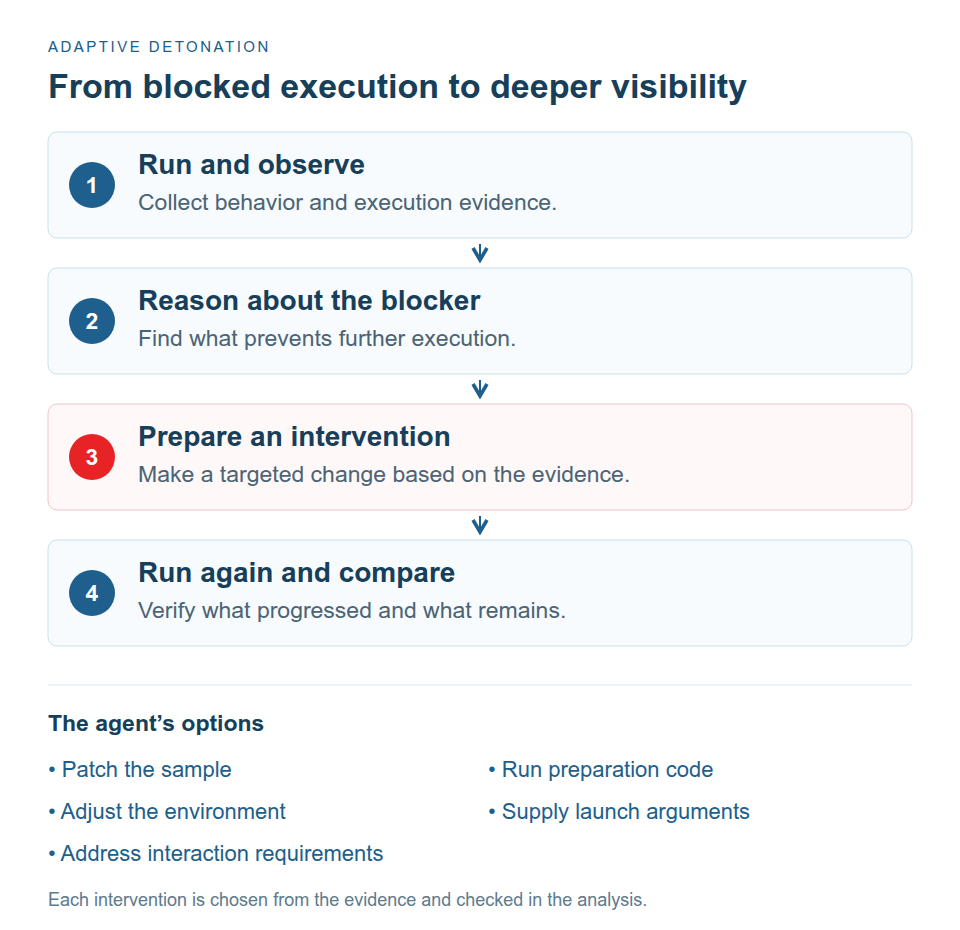
Adaptive Detonation shipped An AI agent capability that runs a sample, identifies what blocked execution, applies a targeted change to the analysis environment or inputs, and re-analyzes the unchanged sample to surface behavior the initial run missed.
Shared capability: Malware sandbox analysis
release
-
Joe Sandbox now adds Adaptive Detonation, an AI agent capability that runs a sample, identifies what blocked execution (evasion check, missing prerequisite, or failure), applies a targeted change, and re-analyzes the sample under the new conditions to surface behavior the initial run missed.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
 The Sandbox That Fights Back: Introducing Adaptive Detonation (2026-11-03) · Nov 2026
· source
· release history
- Analysis reports now include the agent's findings from Adaptive Detonation: what blocked execution, the runtime and code evidence, the recommended action, alternative explanations, and remaining uncertainty. The Sandbox That Fights Back: Introducing Adaptive Detonation (2026-11-03) · Nov 2026 · source · release history
-
The agent can supply missing launch arguments — for example, recovering and injecting the required
S1=1MSI installer property — without modifying the sample package itself. The Sandbox That Fights Back: Introducing Adaptive Detonation (2026-11-03) · Nov 2026 · source · release history - Adaptive Detonation is available as part of Joe Sandbox AI and has been running in Joe Sandbox Cloud Basic. The Sandbox That Fights Back: Introducing Adaptive Detonation (2026-11-03) · Nov 2026 · source · release history
- The agent can run preparation code to create required files, directories, or registry values, or install a missing software dependency such as Python in a location the sample already searches. The Sandbox That Fights Back: Introducing Adaptive Detonation (2026-11-03) · Nov 2026 · source · release history
- The agent can adjust the analysis environment by setting the guest machine's date to a required window or advancing the guest clock (demonstrated by a two-day advance to bypass a file-age loader delay) before re-running the unchanged sample in Joe Sandbox Cloud. The Sandbox That Fights Back: Introducing Adaptive Detonation (2026-11-03) · Nov 2026 · source · release history
Submission status and results retrieval shipped Query the status and results of a previously submitted analysis by its submission ID.
Shared capability: Malware sandbox analysis
Also counts toward: SIEM forwarding
release
- Adds Analysis Workflow diagram, IOC Relationship Map, and an overview executive snapshot diagram to the analysis report Joe Reverser 2.1 Golden Eagle (2026-09-14) · Sep 2026 · source · release history
- Enables downloadable PDF Reports alongside existing HTML reports for archiving, sharing, and case management Joe Reverser 2.1 Golden Eagle (2026-09-14) · Sep 2026 · source · release history
- Adds File Viewer in chat mode to inspect and download generated artifacts like unpacking scripts directly from the analysis experience Joe Reverser 2.1 Golden Eagle (2026-09-14) · Sep 2026 · source · release history
- Added Microsoft Sentinel Integration to push Joe Sandbox analysis results back into Microsoft Sentinel workflows for enriched incident context. Joe Sandbox v44 - Smoke Quartz (2026-01-19) · Jan 2026 · source · release history
example
-
Send suspicious artifacts from Microsoft Sentinel to Joe Sandbox and ingest the behavioral report back into Sentinel.
Configure the 'Joe Sandbox' connector in Microsoft Sentinel workflows, pointing analysis requests to your Joe Sandbox API endpoint.Joe Sandbox v44 - Smoke Quartz (2026-01-19) · Jan 2026 · source -
Show status/results for a submission by ID (read-only).
jbxapi submission info 140
Parallel dual-engine analysis shipped Submit samples simultaneously to both dynamic analysis and agentic reverse engineering engines for comprehensive results.
Shared capability: Malware sandbox analysis
release
- Introduces Parallel Mode to submit the same sample simultaneously to Joe Sandbox (dynamic analysis) and Joe Reverser (agentic reverse engineering) Joe Reverser 2.1 Golden Eagle (2026-09-14) · Sep 2026 · source · release history
Static malware analysis 1 feature Investigation and response since 2026
Agentic reverse engineering analysis shipped Utilize the Joe Reverser engine for autonomous, agentic-based malware and phishing analysis with integrated workflow capabilities.
Shared capability: Static malware analysis
release
-
Releases Joe Reverser 2.1 Golden Eagle, an agentic automated analyst covering malware, phishing campaigns, malicious documents, and web-based threats with enhanced autonomous analysis and reverse engineering.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
 changelog · Sep 2026
· source
· release history
- Improves integration into automated analysis workflows for Joe Reverser's agentic capabilities. changelog · Sep 2026 · source · release history
docs
- Joe Reverser 2.1 Golden Eagle We are proud to announce the release of Joe Reverser 2.1 Golden Eagle , the latest evolution of our agentic automated malware and phishing analyst.Joe Reverser is designed to help security analysts investigate complex malware, phishing campaigns, malicious documents, and web-based… changelog · Sep 2026 · source
Other / not yet classified 6 features Features we have not matched to a capability yet. A suggested match is marked.
Advanced detection capabilities shipped suggested Employ enhanced YARA rules, behavior signatures, malware configuration extractors, and Suricata engine updates to detect sophisticated threats and extract IOCs.
Suggested capability: Threat indicator matching. This is our guess, not confirmed.
release
-
Adds 575 new custom YARA rules to detect ransomware, stealers, RATs, and phishing frameworks.
Joe Sandbox v45 - Green Opal (2026-09-07) · Sep 2026
· source
· release history
- Adds 50 new behavior signatures covering emerging malware families including RatonRAT, REMUS Stealer, EtherHiding, GehennaLocker, PureLogs Stealer, PhantomGate, QuimaRAT, and others. Joe Sandbox v45 - Green Opal (2026-09-07) · Sep 2026 · source · release history
- Adds 55 new malware configuration extractors — including ZigClipper, BlakcSee Stealer, Sirius RAT, OverLordRat, CastleRat, WikiKit, PhantomGate, Remus Stealer, SantaStealer, and GenericBot — to automatically extract IOCs and family configuration data without manual reverse engineering. Joe Sandbox v45 - Green Opal (2026-09-07) · Sep 2026 · source · release history
Phishing and web analysis agent shipped suggested Analyze phishing URLs and malicious web content using specialized agents, proxies, and dynamic DOM extraction to bypass detection and uncover threats.
Suggested capability: Malware sandbox analysis. This is our guess, not confirmed.
release
-
Improves DOM extraction and phishing detection for better visibility into dynamic web content, obfuscated scripts, and redirect-based phishing pages.
Joe Sandbox v45 - Green Opal (2026-09-07) · Sep 2026
· source
· release history
- Improves QR code reader analysis to uncover embedded URLs and data in QR-based phishing samples and documents. Joe Sandbox v45 - Green Opal (2026-09-07) · Sep 2026 · source · release history
example
-
Analyze a phishing URL using residential proxies in Joe Sandbox Cloud Pro to bypass bot detection.
Use the Joe Sandbox Cloud Pro interface to configure proxy settings (SOCKS/HTTP) for the analysis job.Joe Sandbox v44 - Smoke Quartz (2026-01-19) · Jan 2026 · source
Analysis platform integration shipped suggested Integrate with external security platforms, such as Microsoft Sentinel, to synchronize analysis submissions and enrich incident context.
Suggested capability: Malware sandbox analysis. This is our guess, not confirmed.
Also counts toward: SIEM forwarding
release
- Added Microsoft Sentinel Integration to push Joe Sandbox analysis results back into Microsoft Sentinel workflows for enriched incident context. Joe Sandbox v44 - Smoke Quartz (2026-01-19) · Jan 2026 · source · release history
example
-
Send suspicious artifacts from Microsoft Sentinel to Joe Sandbox and ingest the behavioral report back into Sentinel.
Configure the 'Joe Sandbox' connector in Microsoft Sentinel workflows, pointing analysis requests to your Joe Sandbox API endpoint.Joe Sandbox v44 - Smoke Quartz (2026-01-19) · Jan 2026 · source
Agent guidance modes shipped Provide specific operational modes for analysis agents, such as guiding them toward objectives without predefined workflows.
release
- Adds Skill Only Mode to guide the agent toward specific objectives without predefined workflows Joe Reverser 1.0.0 Silver Wolf (2026-03-05) · Mar 2026 · source · release history
File format expansion shipped Extend analysis support to include common office document formats such as DOC/DOCX, XLS/XLSX, and PPT/PPTX.
release
- Adds analysis support for DOC/DOCX, XLS/XLSX, and PPT/PPTX file formats Joe Reverser 1.0.0 Silver Wolf (2026-03-05) · Mar 2026 · source · release history
Server connectivity check shipped Check whether the Joe Sandbox server is reachable and online.
example
-
Query whether the Joe Sandbox server is online (read-only).
jbxapi server online
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
3 commands for Joe Security (Joe Sandbox), each with where it came from. This tool has no source analysis yet, so there is no option reference and no captured run beside them.
No command matches.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for Joe Security (Joe Sandbox), each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Joe Security (Joe Sandbox) puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Website history
joesecurity.org, every changeJoe Security's home page and 2 more pages as they looked each month from September 2021 to October 2026: 16 renders, 1 change of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Releases
6 entries
No entries match these filters.
- November 20261
- September 20263
- March 20261
- January 20261
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →