OWASP ZAP
2.16.1 open-sourceThe section your link pointed to isn't on OWASP ZAP's page any more, so we've brought you to the top.
OWASP ZAP is a free, open-source web app scanner that automatically finds security vulnerabilities in web applications during development and testing.
env:
  contexts:
    - name: "ai-auth-context"
      urls:
        - "https://www.example.com"
      authentication:
        method: "ai"
        parameters:
          loginPageUrl: "https://www.example.com/login"
          browserId: "firefox-headless"
          loginPageWait: 5
          hint: "Set the domain dropdown to Project1 before clicking Next."
      verification:
        method: "autodetect"
      sessionManagement:
        method: "autodetect"
      users:
        - name: "test-user"
          credentials:
            username: "[email protected]"
            password: "${AUTH_PASSWORD}"
jobs:
  - type: llm-config
    parameters:
      defaultProvider: "my-provider"
      defaultModel: "my-model"
      providers:
        - name: "my-provider"
          type: "OPENAI_COMPATIBLE"
          apiKey: "${LLM_API_KEY}"
          endpoint: "https://llm.example.com/v1"
          models:
            - "my-model"
  - type: "requestor"
    parameters:
      user: "test-user"
      requests:
        - url: "https://www.example.com/"
          method: "GET"
          responseCode: 200
- type: insights
  parameters:
    exitAutoLevel: high
- type: spiderClient
  parameters:
    runOnlyIfModern: true
zap_get_history body_offset=0 max_body_chars=2000
Summary
OWASP ZAP is an open-source web application scanner, free to use under the Apache 2 licence, that intercepts and inspects traffic between a browser and a web app to find security vulnerabilities as they're built and tested. It runs as a desktop proxy on a developer's or tester's machine, with a REST APIREST APIA web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. and automation framework for wiring scans into a pipeline, so it works equally as a manual tool and as an unattended CI step. Its README describes it as suited both to developers checking their own applications during testing and to experienced pentesters running manual assessments, and calls itself the most widely used tool of its kind. The project traces back to a 2010 first commit and remains active, with 292 contributors and 176 commits in the past year across 36 releases.
OWASP ZAP is a free, open-source web app scanner that automatically finds security vulnerabilities in web applications during development and testing.
How OWASP ZAP helps
Which of my web application's pages and parameters are exposed to known attack patterns like injection or cross-site scripting?
runs active scan rules against traffic captured through the proxy, sending crafted requests and flagging responses that match known vulnerability signatures, tagged by alert and location
What does my application actually expose to a browser that I haven't accounted for?
sits as a proxy between browser and app, recording every request and response passing through so hidden endpoints, parameters and forms surface without needing source access
Are the pages my testers can see the same ones an automated crawl finds?
runs an AJAX-aware spider that executes client-side scripts to discover links a traditional crawler would miss, adding them to the same site map as manual browsing
Can my authentication flow be scanned the same way as everything else?
offers authentication handling that detects or replays login requests and session tokens so scans continue past the login page instead of stopping at it
Did last night's pipeline scan turn up anything my last release didn't have?
records alerts per run through the automation framework, so comparing job output across builds shows which vulnerabilities are newly present
Is my scan policy consistent between what a tester runs by hand and what the pipeline runs unattended?
the same rule configuration and automation framework jobs drive both the desktop proxy and the unattended run, so a scan defined once produces the same alerts whichever way it's triggered
Languages
Features
Built from OWASP ZAP's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- OWASP ZAP covers 2 of the 8 vulnerability assessment methods capabilities we track.
What OWASP ZAP offers you
- CI/CD pipeline integration3
- REST API2
- Scripting language support2
- Scheduled jobs1
No capabilities match.
Web vulnerability scanning 7 features Vulnerability assessment methods since 2025
Active scanning verified Runs active scans against a target web application to actively probe for vulnerabilities, with controls over scan behaviour such as request delay and parameter exclusions.
Shared capability: Web vulnerability scanning
release
-
Adds an option to send requests when importing a HAR file in the Import/Export add-on, including via the Automation Framework and API.
 announced · Sep 2026
· source
· release history
- Deprecated endpoint GET /JSON/ascan/view/optionDelayInMs/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/ascan/action/setOptionDelayInMs/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/ascan/view/optionExcludedParamList/ (still works) 2.16.1 · Aug 2026 · source · release history
-
Adds
sequence-activeScanjob to the Automation Framework to perform active scanning on imported sequences. 2.16.0 · Jan 2025 · source · release history
docs
- Web app scanner that automatically finds security vulnerabilities during development, testing, and manual pentesting.
example
-
Cap the number of messages imported when pulling in a large OpenAPI spec, to keep scan sessions manageable during auth or access-control testing.
In the ZAP OpenAPI Import dialogue, set maxMessages to the desired limit (e.g. 100) before importing — or supply the same field via the Automation Framework job or API call.announced · Sep 2026 · source -
Use the MCP Integration to page through large HTTP response bodies in history without overwhelming the LLM context window.
zap_get_history body_offset=0 max_body_chars=2000announced · Sep 2026 · source
api 90 total
-
GET /JSON/ascan/view/optionExcludedParamList/· source · full API surface -
GET /JSON/ascan/action/scanAsUser/· source · full API surface -
GET /JSON/ascan/view/optionShowAdvancedDialog/· source · full API surface -
GET /JSON/ascan/action/stopAllScans/· source · full API surface -
GET /JSON/ascan/view/optionPromptToClearFinishedScans/· source · full API surface -
GET /JSON/ascan/action/setOptionAddQueryParam/· source · full API surface
Spider (traditional crawler) verified Crawls a web application automatically to discover pages and endpoints that should be included in subsequent scans.
Shared capability: Web vulnerability scanning
Also counts toward: REST API
release 7 total
- Retires the AJAX Spider and DOM XSS Active Scan Rule add-ons from nightly and weekly Docker releases; the Quickstart tab now defaults to the headless Firefox Client Spider crawler, and bundled Automation Framework profiles and the Chrome AF plan have been switched to the Client Spider. announced · Oct 2026 · source · release history
-
The AJAX Spider and DOM XSS add-ons are no longer available in nightly and weekly releases; workflows depending on either add-on will break on those release channels.
announced · Sep 2026
· source
· release history
- AJAX Spider and DOM XSS Active Scan Rule add-ons are removed from nightly and weekly Docker releases; existing Automation Framework and API jobs continue working, now backed by the Client Spider. announced · Sep 2026 · source · release history
- Deprecated endpoint GET /JSON/spider/view/optionDomainsAlwaysInScope/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/spider/view/optionDomainsAlwaysInScopeEnabled/ (still works) 2.16.1 · Aug 2026 · source · release history
- Includes Client Spider as standard via the Client Integration add-on, enabling DOM-based crawling that supersedes AJAX Spider capabilities. 2.16.0 · Jan 2025 · source · release history
docs
- Alert Filter LLM Support Authentication Helper Automation Framework Support LLM Support LLM Chat LLM MCP Support seen Aug 2026 · source
api 72 total
-
GET /JSON/spider/action/modifyDomainAlwaysInScope/· source · full API surface -
GET /JSON/spider/view/optionLogoutAvoidance/· source · full API surface -
GET /JSON/spider/action/setOptionHandleParameters/· source · full API surface -
GET /JSON/spider/action/setOptionParseDsStore/· source · full API surface -
GET /JSON/spider/action/pauseAllScans/· source · full API surface -
GET /JSON/spider/view/optionMaxParseSizeBytes/· source · full API surface
Browser-based scanning via Selenium verified Drives a real browser during crawling and scanning to reach content that requires JavaScript execution, using configurable browser drivers.
Shared capability: Web vulnerability scanning
Also counts toward: REST API
release
- Deprecated endpoint GET /JSON/selenium/view/optionPhantomJsBinaryPath/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/selenium/action/setOptionIeDriverPath/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/selenium/view/optionIeDriverPath/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/selenium/action/setOptionPhantomJsBinaryPath/ (still works) 2.16.1 · Aug 2026 · source · release history
api 55 total
-
GET /JSON/selenium/view/getBrowserArguments/· source · full API surface -
GET /JSON/ajaxSpider/action/removeExcludedElement/· source · full API surface -
GET /JSON/ajaxSpider/view/optionBrowserId/· source · full API surface -
GET /JSON/selenium/view/optionFirefoxDriverPath/· source · full API surface -
GET /JSON/ajaxSpider/action/setOptionBrowserId/· source · full API surface -
GET /JSON/ajaxSpider/view/optionLogoutAvoidance/· source · full API surface
Passive scanning verified Monitors HTTP traffic passively as it passes through the proxy, flagging issues without sending additional attack traffic to the target.
Shared capability: Web vulnerability scanning
release
-
ZAP's Passive scanner rules (v77) add a Server Side Technology Version with Known Vulnerabilities rule that checks technology versions disclosed in response headers against known vulnerabilities, initially covering PHP versions via php-src security advisories.
 announced · Nov 2026
· source
· release history
- Updates Passive scanner rules v76 so the Content Security Policy scan rule analyzes all active CSP headers and META policies together using browser-style intersection. announced · Oct 2026 · source · release history
- Adds a Global Scan Policy dialog (accessible in dev mode) as Phase 1 of the Global Scan Policy Manager, unifying configuration of HTTP passive scan rules, active scan rules, script-based active and passive scan rules, and policy migration from per-context scan policies into a single… announced · Oct 2026 · source · release history
- Deprecated endpoint GET /JSON/pscan/view/currentRule/ (still works) 2.16.1 · Aug 2026 · source · release history
api 17 total
-
GET /JSON/pscan/view/recordsToScan/· source · full API surface -
GET /JSON/pscan/action/setEnabled/· source · full API surface -
GET /JSON/pscan/view/scanOnlyInScope/· source · full API surface -
GET /JSON/pscan/action/disableAllTags/· source · full API surface -
GET /JSON/pscan/view/currentRule/· source · full API surface -
GET /JSON/pscan/action/disableScanners/· source · full API surface
Client Spider shipped Enables DOM-based crawling via a new Client Spider integration standard in the Client Integration add-on, superseding AJAX Spider capabilities.
Shared capability: Web vulnerability scanning
release
-
ZAP's Client Side Integration add-on (v0.32.0) now stands in for the AJAX Spider's
spiderAjaxautomation job andajaxSpiderAPI using the Client Spider when the AJAX Spider add-on is not installed.
announced · Nov 2026
· source
· release history
- Includes Client Spider as standard via the Client Integration add-on, enabling DOM-based crawling that supersedes AJAX Spider capabilities. 2.16.0 · Jan 2025 · source · release history
example
-
Run the Client Spider only on pages ZAP has already flagged as modern web apps, avoiding unnecessary crawl overhead on traditional server-rendered sites.
- type: spiderClient parameters: runOnlyIfModern: trueannounced · Nov 2026 · source
Automation Framework Client Spider Job shipped Adds the `spiderClient` job to the Automation Framework to execute the new Client Spider integration.
Shared capability: Web vulnerability scanning
release
-
ZAP's Client Side Integration add-on (v0.32.0) adds a
runOnlyIfModernoption to thespiderClientAutomation Framework job to run the Client Spider only when a Modern Web Application alert has been raised.
announced · Nov 2026
· source
· release history
-
Adds
spiderClientjob to the Automation Framework to run the new Client Spider integration. 2.16.0 · Jan 2025 · source · release history
Browser Background Request Filtering shipped Provides configuration to control how browser background requests are handled during scanning, with options to hide them.
Shared capability: Web vulnerability scanning
release
-
Adds an option to control how browser background requests are handled in the Network add-on, defaulting to hide.
announced · Sep 2026
· source
· release history
Credentialed vulnerability scanning 2 features Vulnerability assessment methods since 2025
Authentication helper shipped Provides assisted configuration of authentication methods, including OAuth 2.0 client_credentials and password grant types with automatic refresh token handling and session management autodetection.
Shared capability: Credentialed vulnerability scanning
Also counts toward: CI/CD pipeline integration
release 10 total
-
ZAP's Authentication Helper add-on (v0.43.0) adds
typeandcountparameters to the diagnostics automation job, retaining only the last failed attempt withauth_on_failureor a rolling window of failures withauth_failure_rolling.
announced · Nov 2026
· source
· release history
-
ZAP's Automation Framework (v0.61.0) adds
oauth2authentication method support and allows defining how long a plan can run. announced · Nov 2026 · source · release history -
ZAP's Authentication Helper add-on (v0.43.0) now has an OAuth2 authentication method supporting the
client_credentialsandpasswordgrant types, configurable via the desktop UI, the Automation Framework, and the API.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Nov 2026 · source · release history -
Adds
oauth2authentication method to the Automation Framework viamethod: 'oauth2'underauthentication, supportinggrantType,tokenEndpoint,clientId,clientSecret,clientAuthMethod,scope,accessTokenField,refreshTokenField, andextraTokenParamsparameters.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Oct 2026 · source · release history - Adds OAuth2 Authentication option to the Desktop UI Authentication screen, selectable from the authentication pulldown on a Context. announced · Oct 2026 · source · release history
-
Supports
client_credentials(default) andpassword(resource owner password credentials) non-interactive grant types against a singletokenEndpoint. announced · Oct 2026 · source · release history
docs
example
-
Verify that
oauth2Authenticationis available on your ZAP instance before configuring it.curl -X GET "http://localhost:8080/JSON/authentication/view/getSupportedAuthenticationMethods/"announced · Oct 2026 · source -
Set OAuth2 authentication on context ID 1 via the ZAP API in a CI pipeline without the desktop UI.
curl -X POST "http://localhost:8080/JSON/authentication/action/setAuthenticationMethod/" -d \…announced · Oct 2026 · source -
Configure OAuth2 client-credentials authentication in a ZAP Automation Framework plan to scan an API that requires a bearer token.
env: contexts: - name: "oauth2-context" urls: - "https://api.example.com" includePaths: - "https://api\\.example\\.com.*" authentication: method: "oauth2" parameters: grantType: "client_credentials"…announced · Oct 2026 · source
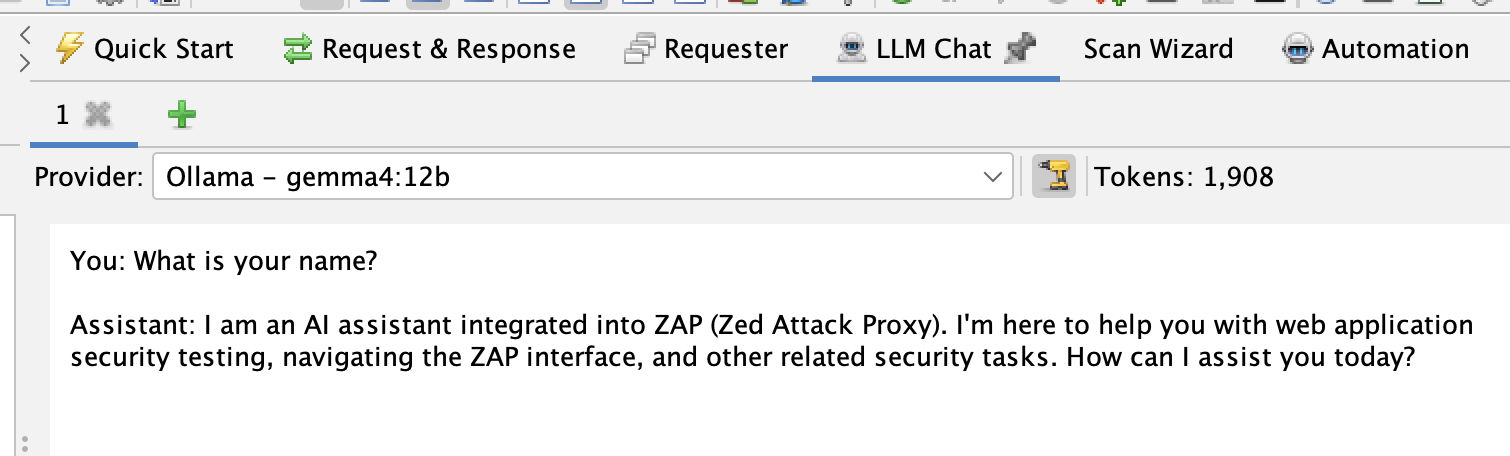
AI Assisted Authentication shipped Uses an LLM to drive a real browser through multi-step login flows, converting a successful session into a reusable Zest script, with support for free-text hints, interactive testing, Automation Framework integration, and a dedicated monitoring tab.
Shared capability: Credentialed vulnerability scanning
Also counts toward: Scripting language support
release
-
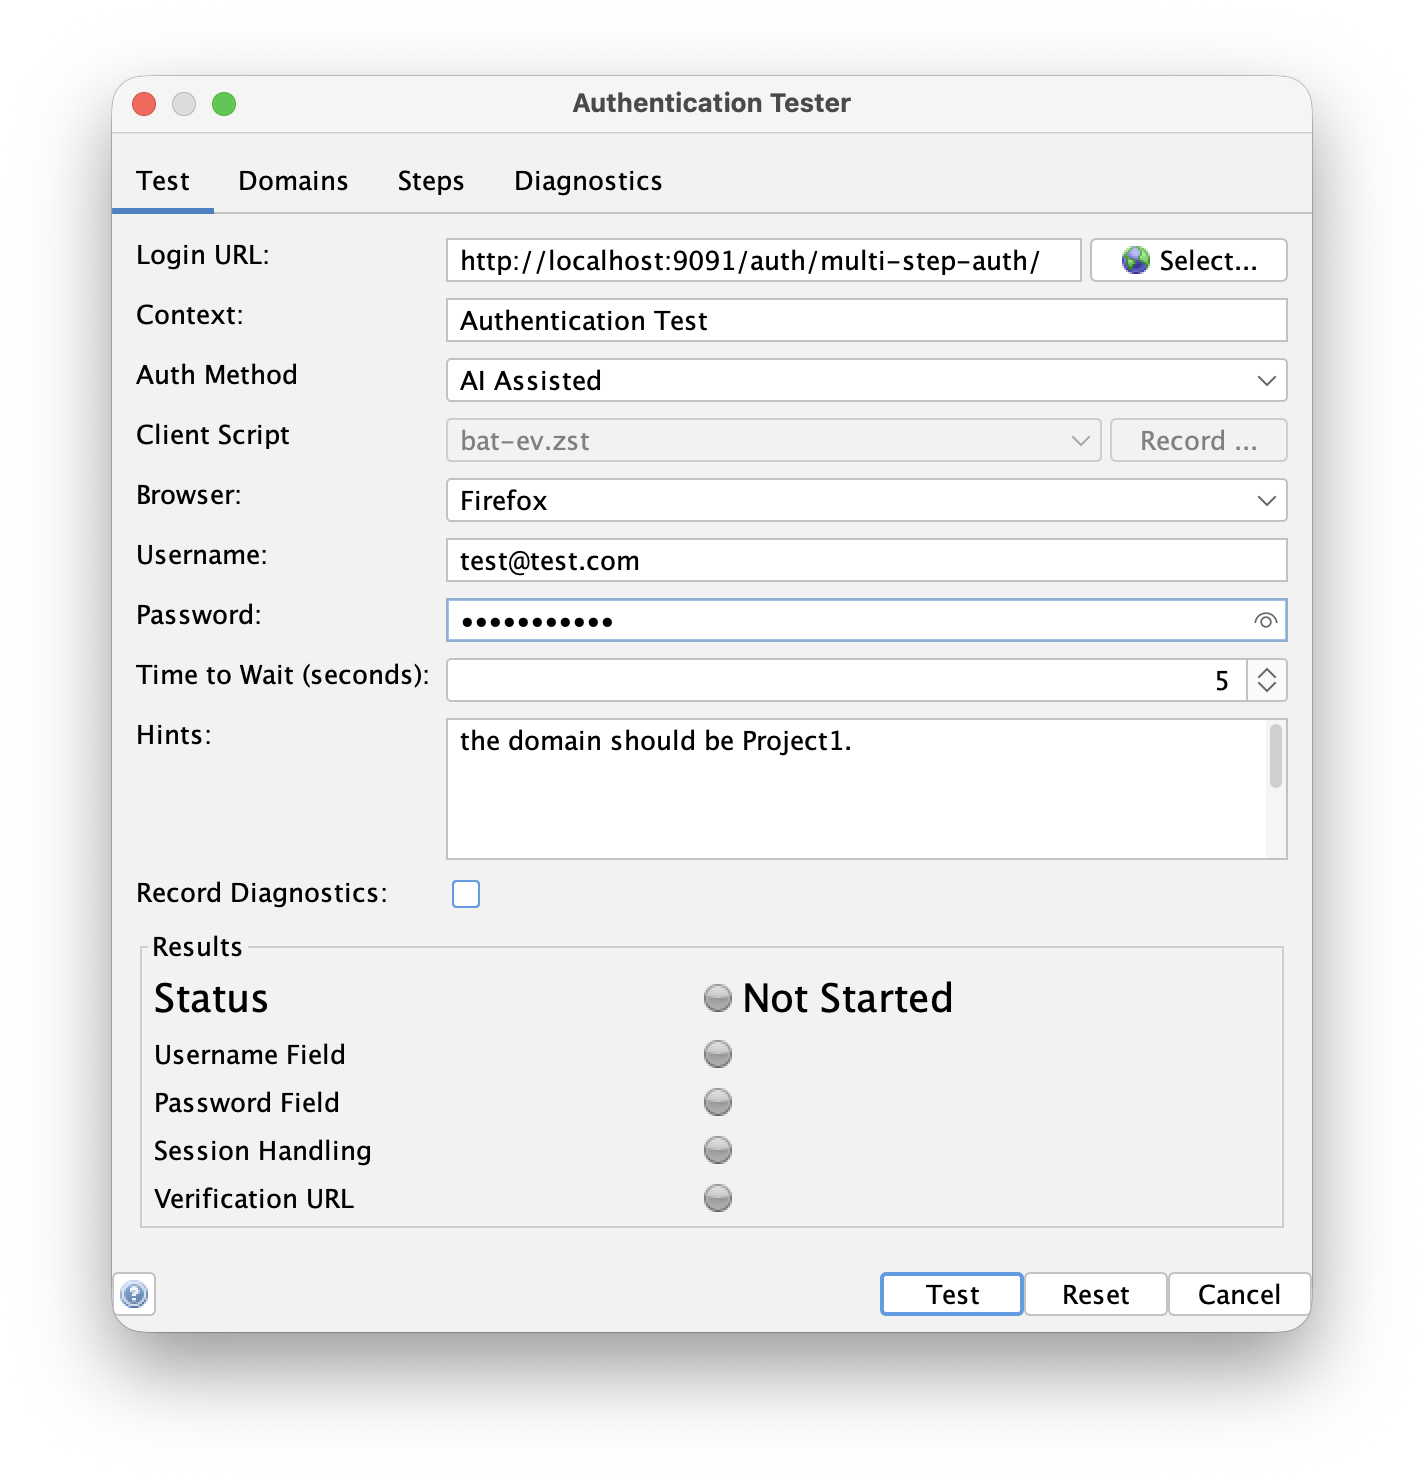
Try AI Assisted Authentication interactively by opening the Authentication Tester from Tools menu or the Ctrl+T shortcut, selecting AI Assisted as the Auth Method, entering credentials and an optional hint, then pressing Test.
 announced · Nov 2026
· source
· release history
-
Supply free-text
hintguidance (for example, 'Set the domain dropdown to Project1 before clicking Next.') to steer the LLM past steps that cannot be inferred from the page alone. announced · Nov 2026 · source · release history - OWASP ZAP adds an AI Assisted Authentication method that uses an LLM to drive a real browser through multi-step login flows that Browser Based Authentication heuristics cannot handle, then automatically converts the successful session into a reusable Client Script Authentication Zest script. announced · Nov 2026 · source · release history
-
Automate complex login flows in the Automation Framework by setting the authentication method to
aiwith parametersloginPageUrl,browserId,loginPageWait, and optionalhintunder theauthenticationblock.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Nov 2026 · source · release history - Monitor each LLM authentication step — page description sent, actions chosen, and reasoning — in the new AI Assisted Auth tab inside the LLM Chat tab. announced · Nov 2026 · source · release history
example
-
Open the Authentication Tester interactively to test a complex login page with AI assistance and optional hints before committing to automation.
1. Ensure the LLM Support add-on is configured with a provider. 2. Open Tools > Authentication Tester (or press Ctrl+T / Cmd+T on macOS). 3. Set Auth Method to 'AI Assisted'. 4.announced · Nov 2026 · source -
Run a scan against an app with a complex multi-step login that Browser Based Authentication cannot handle, letting the LLM work out the flow once and generate a reusable script.
env: contexts: - name: "ai-auth-context" urls: - "https://www.example.com" authentication: method: "ai" parameters: loginPageUrl: "https://www.example.com/login" browserId: "firefox-headless"…announced · Nov 2026 · source
Other / not yet classified 14 features Features we have not matched to a capability yet. A suggested match is marked.
Upstream proxy configuration verified Configures an upstream proxy chain so that ZAP's outbound traffic is routed through another proxy, including authentication and SOCKS support.
release 31 total
-
ZAP's Network add-on now notifies other add-ons when an outbound proxy is enabled (v0.30.0) and when requests fail to send, such as DNS errors, connection refused, or timeouts (v0.32.0).
announced · Nov 2026
· source
· release history
- Deprecated endpoint GET /JSON/core/view/optionProxyExcludedDomains/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/core/action/setOptionProxyChainSkipName/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/core/action/addProxyChainExcludedDomain/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /OTHER/core/other/setproxy/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/core/action/setOptionProxyChainUserName/ (still works) 2.16.1 · Aug 2026 · source · release history
api 51 total
-
GET /JSON/core/view/optionProxyChainPort/· source · full API surface -
GET /JSON/core/view/optionProxyExcludedDomainsEnabled/· source · full API surface -
GET /JSON/network/action/setPassThroughEnabled/· source · full API surface -
GET /JSON/network/action/setHttpProxy/· source · full API surface -
GET /JSON/network/view/getRateLimitRules/· source · full API surface -
GET /JSON/network/view/getPassThroughs/· source · full API surface
Core HTTP session and connection settings verified Sets global HTTP connection options such as user agent string, request timeout, cookie handling, HTTP state tracking, and DNS TTL.
release 13 total
-
Renames Fuzzer payload replacement strategies to Cluster Bomb and Pitchfork in the UI (previously Depth First and Breadth First).
announced · Sep 2026
· source
· release history
- Deprecated endpoint GET /JSON/core/view/optionDnsTtlSuccessfulQueries/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/core/view/optionSingleCookieRequestHeader/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/core/action/setOptionSingleCookieRequestHeader/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/core/action/setOptionDnsTtlSuccessfulQueries/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/core/view/optionDefaultUserAgent/ (still works) 2.16.1 · Aug 2026 · source · release history
docs
- Headline Statistics for July 2026 13,295,706 4,370,943 3,009,052,957 5,443,497,988 - Including ZAP Starts, Direct Downloads, Docker Pulls, and User Group Posts seen Aug 2026 · source
api 38 total
-
GET /JSON/core/action/setOptionSingleCookieRequestHeader/· source · full API surface -
GET /JSON/network/view/getConnectionTimeout/· source · full API surface -
GET /JSON/core/action/setOptionHttpStateEnabled/· source · full API surface -
GET /JSON/network/view/isUseGlobalHttpState/· source · full API surface -
GET /JSON/core/action/loadSession/· source · full API surface -
GET /JSON/core/action/setMode/· source · full API surface
Alert management verified Displays all findings raised during scanning, and lets users summarise or delete individual alerts or clear them all.
release 10 total
-
Supports suppressing known-patched servers via an Alert Filter matching URL, the PHP Version with Known Vulnerabilities alert name, and the specific version string evidence (e.g.
PHP/8.1.2), configurable globally, in a context, or in the Automation Framework for CI/CD pipelines. announced · Oct 2026 · source · release history -
Adds a new LLM Support add-on to OWASP ZAP, officially launched in August 2026.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
announced · Sep 2026
· source
· release history
- Adds LLM Support add-on (v0.0.1) connecting ZAP to Claude (Anthropic), Google Gemini, Azure OpenAI, Ollama, and OpenAI Compatible endpoints, with a tabbed LLM Chat panel and integration with the MCP add-on. announced · Sep 2026 · source · release history
- Deprecated endpoint GET /JSON/core/view/alerts/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/core/view/alertsSummary/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/core/action/deleteAllAlerts/ (still works) 2.16.1 · Aug 2026 · source · release history
example
-
Suppress a false-positive alert on a host where you know PHP security backports have been applied, without silencing future version changes.
In the ZAP UI, go to Analyse > Alert Filters > Add, set the URL regex to the target site (e.g.announced · Oct 2026 · source
api 30 total
-
GET /JSON/core/action/setOptionMaximumAlertInstances/· source · full API surface -
GET /JSON/alert/action/deleteAllAlerts/· source · full API surface -
GET /JSON/core/view/alertsSummary/· source · full API surface -
GET /JSON/alert/action/deleteAlert/· source · full API surface -
GET /JSON/alert/view/alert/· source · full API surface -
GET /JSON/core/view/alerts/· source · full API surface
HTTP traffic export verified suggested Exports captured HTTP messages and scan results in HAR or XML format for use in external tools or reports.
Suggested capability: Web vulnerability scanning. This is our guess, not confirmed.
release 11 total
-
Adds
maxMessagesoption to GraphQL Support, Import/Export (HAR), OpenAPI Support, Postman Support, and SOAP Support add-ons to cap the number of messages imported during testing.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
announced · Sep 2026
· source
· release history
-
Adds
zap_list_resources,zap_read_resource, andzap_get_historytools to the MCP Integration add-on;zap_get_historysupports body paging viabody_offsetandmax_body_charsfields. announced · Sep 2026 · source · release history - Adds an option to control how browser background requests are handled in the Network add-on, defaulting to hide. announced · Sep 2026 · source · release history
- Deprecated endpoint GET /OTHER/core/other/messagesHarById/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /OTHER/core/other/xmlreport/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /OTHER/core/other/messagesHar/ (still works) 2.16.1 · Aug 2026 · source · release history
api 27 total
-
GET /OTHER/exim/other/sendHarRequest/· source · full API surface -
GET /OTHER/core/other/messageHar/· source · full API surface -
GET /JSON/reports/view/templates/· source · full API surface -
GET /JSON/exim/action/importZapLogs/· source · full API surface -
GET /OTHER/core/other/fileDownload/· source · full API surface -
GET /JSON/search/view/messagesByUrlRegex/· source · full API surface
TLS/SSL certificate management verified Generates and downloads a root CA certificate for installation in browsers, and manages client certificates used when the target requires mutual TLS authentication.
release
-
Adds an option to support client certificates programmatically in the Network add-on.
announced · Sep 2026
· source
· release history
- Deprecated endpoint GET /JSON/core/action/disableClientCertificate/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /OTHER/core/other/rootcert/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/core/action/generateRootCA/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/core/action/enablePKCS12ClientCertificate/ (still works) 2.16.1 · Aug 2026 · source · release history
docs
- Alert Filter LLM Support Authentication Helper Automation Framework Support LLM Support LLM Chat LLM MCP Support seen Aug 2026 · source
api 13 total
-
GET /OTHER/core/other/rootcert/· source · full API surface -
GET /JSON/network/view/getRootCaCertValidity/· source · full API surface -
GET /JSON/core/action/disableClientCertificate/· source · full API surface -
GET /JSON/network/action/setRootCaCertValidity/· source · full API surface -
GET /JSON/network/action/generateRootCaCert/· source · full API surface -
GET /OTHER/network/other/rootCaCert/· source · full API surface
Local and additional proxy listeners verified Adds or removes extra local proxy listeners beyond the default, allowing traffic from multiple sources or interfaces to be intercepted.
release
- Deprecated endpoint GET /JSON/localProxies/action/addAdditionalProxy/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/localProxies/action/removeAdditionalProxy/ (still works) 2.16.1 · Aug 2026 · source · release history
- Deprecated endpoint GET /JSON/localProxies/view/additionalProxies/ (still works) 2.16.1 · Aug 2026 · source · release history
docs
- Alert Filter LLM Support Authentication Helper Automation Framework Support LLM Support LLM Chat LLM MCP Support seen Aug 2026 · source
api 9 total
-
GET /JSON/network/action/removePassThrough/· source · full API surface -
GET /JSON/localProxies/view/additionalProxies/· source · full API surface -
GET /JSON/localProxies/action/removeAdditionalProxy/· source · full API surface -
GET /JSON/network/action/addLocalServer/· source · full API surface -
GET /JSON/localProxies/action/addAdditionalProxy/· source · full API surface -
GET /JSON/network/action/setAliasEnabled/· source · full API surface
Zest script recorder and in-browser editor shipped Allows recording, viewing, editing, replaying, and stepping through Zest scripts directly in the browser, including controls to load, save, or clear scripts and modify statement locators with undo/redo support.
release
-
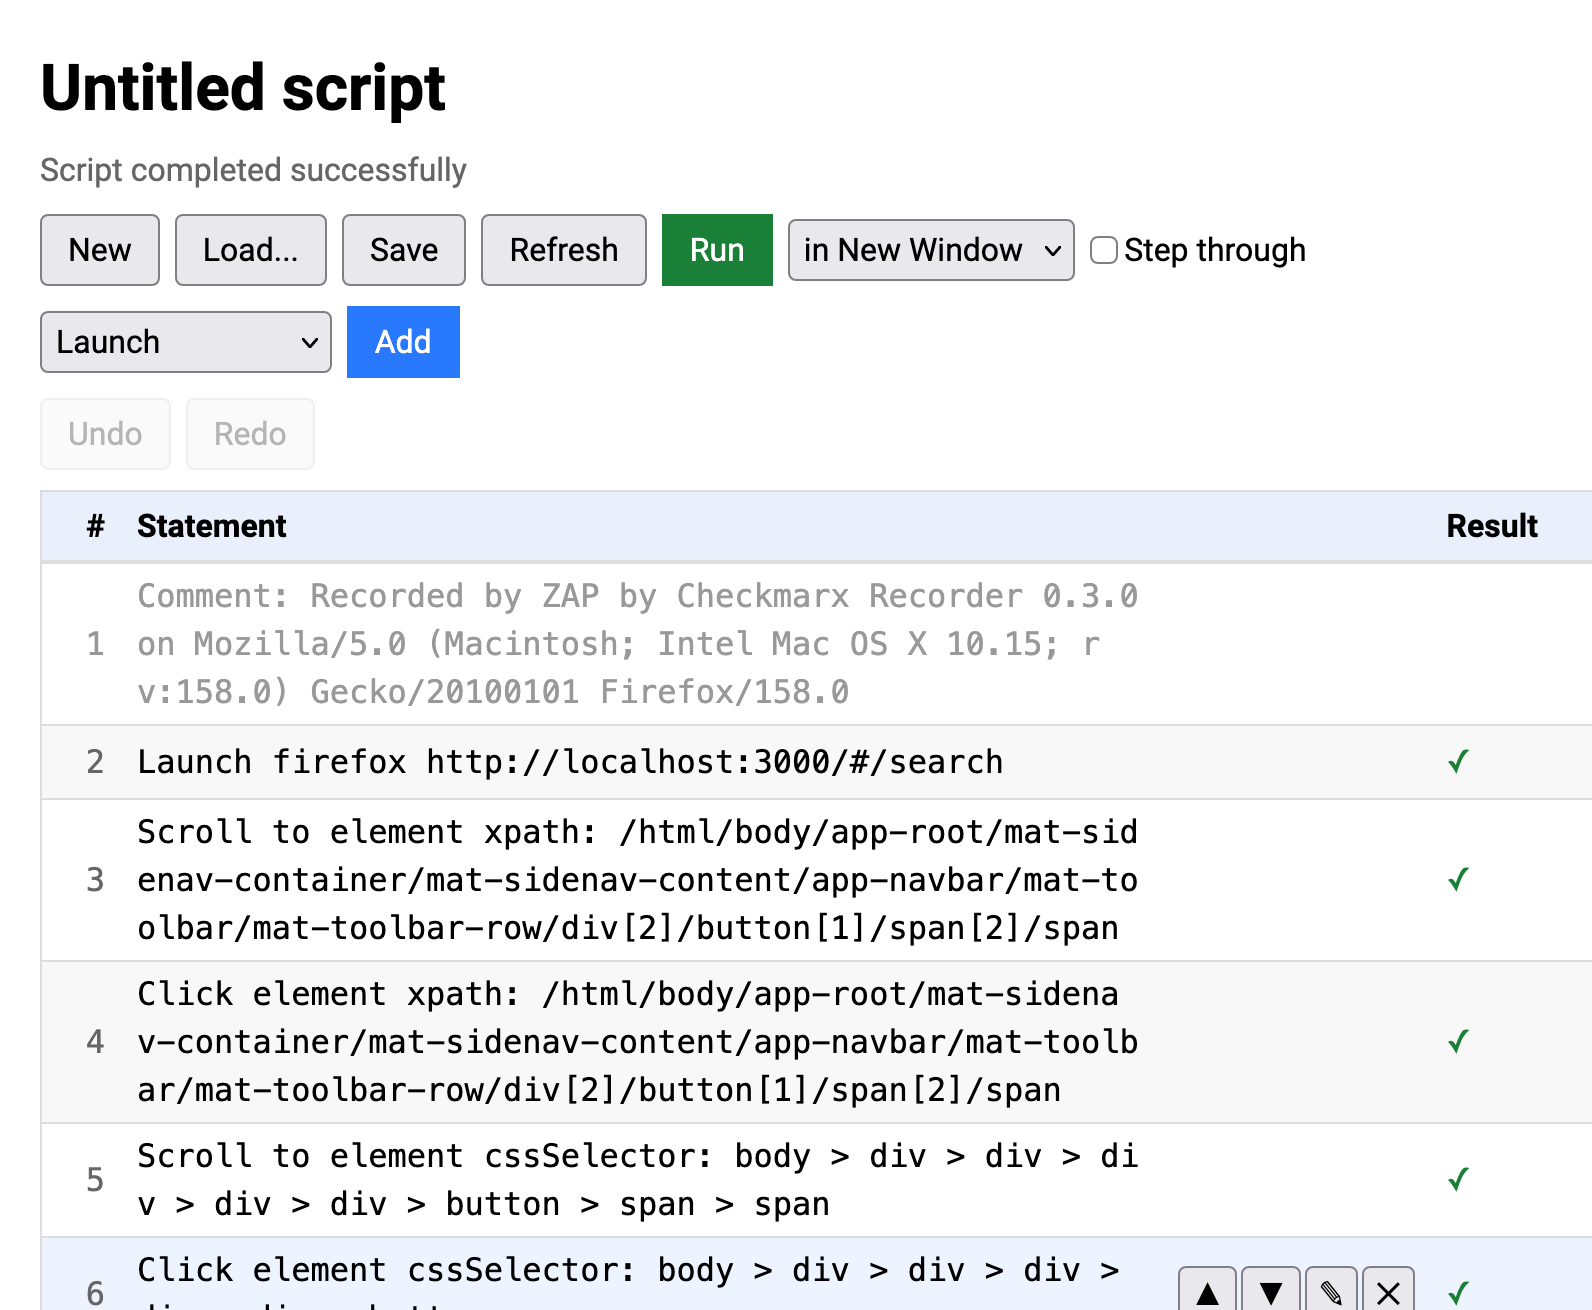
ZAP's Browser Extension (v0.3.0, included in Client Side Integration v0.34.0) adds a Script Viewer that lets you see, edit, replay (including step-by-step), load, and save a Zest script without leaving the browser.
announced · Nov 2026
· source
· release history
-
Adds Load, Save, and New controls in the Script Viewer to open Zest scripts from disk, download the current script, or clear and start fresh.
 announced · Oct 2026
· source
· release history
- Available in both the full ZAP Browser Extension and the standalone Recorder; users launching from ZAP must update the Client Side Integration add-on. announced · Oct 2026 · source · release history
- Adds a View Script button to the ZAP Browser Extension popup that opens the recorded Zest script in its own tab, updating statement-by-statement while recording.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Oct 2026 · source · release history
- Adds Run in New Window and Run in New Tab replay options to execute a Zest script directly in the browser, with a step-through mode (Step / Next) for statement-by-statement inspection. announced · Oct 2026 · source · release history
-
Enables in-browser editing of recorded Zest script statements — including changing locator types (
id,cssSelector,xpath,className,name,linkText,partialLinkText,tagName), reordering, deleting, and adding new statements — with Undo/Redo support. announced · Oct 2026 · source · release history
example
-
Fix a brittle link locator in a saved Zest script by switching it to
partialLinkTextwhen link text includes a variable counter.1. Click 'View Script' in the extension popup, then use 'Load' to open the saved .zst file from disk. 2. Hover over the relevant statement row and click its Edit button. 3.announced · Oct 2026 · source -
Verify a recorded login flow is robust before using it in ZAP — step through each statement one at a time to confirm element locators resolve correctly.
1. Update to version 0.3.0 of the ZAP Browser Extension or standalone Recorder. 2. Record your login flow as normal. 3. Click 'View Script' in the extension popup — the Script Viewer tab opens. 4.announced · Oct 2026 · source
LLM Chat and MCP Support shipped Allows connecting the cyber tool to various LLM endpoints (such as Claude, Gemini, or Ollama) via a dedicated chat interface and Model Context Protocol integration.
release
-
Trigger AI-assisted login programmatically via the
aiAssistedAuthenticationaction in the authentication API.
announced · Nov 2026
· source
· release history
-
Use the
llm-configjob in the Automation Framework to configure a provider, specifyingdefaultProvider,defaultModel, and aproviderslist withtype,apiKey,endpoint, andmodelsfields. announced · Nov 2026 · source · release history -
ZAP's LLM Support add-on (v0.1.0) adds an Automation Framework job
llm-configto configure LLM providers.
announced · Nov 2026
· source
· release history
-
Adds LLM Support add-on (v0.0.1) connecting ZAP to Claude (Anthropic), Google Gemini, Azure OpenAI, Ollama, and OpenAI Compatible endpoints, with a tabbed LLM Chat panel and integration with the MCP add-on.
announced · Sep 2026
· source
· release history
- AJAX Spider and DOM XSS Active Scan Rule add-ons are removed from nightly and weekly Docker releases; existing Automation Framework and API jobs continue working, now backed by the Client Spider. announced · Sep 2026 · source · release history
Server-side technology vulnerability detection shipped suggested Raises alerts for server-side technologies (currently PHP) with known CVE-based vulnerabilities, rated by severity, with automated weekly updates from official security advisories.
Suggested capability: Vulnerability database matching. This is our guess, not confirmed.
Also counts toward: Scheduled jobs, Scripting language support
release
- Raises a PHP Version with Known Vulnerabilities alert scoped to one alert per site/technology/version, risk-rated by the most severe applicable CVE, listing all affected CVEs with severity and links to a new PHP Known Vulnerabilities help page.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Oct 2026 · source · release history
- Keeps the PHP vulnerability list current via a weekly automated job that pulls from the official php-src GitHub security advisories and raises a pull request to update the add-on. announced · Oct 2026 · source · release history
- Designed to support additional server-side technologies beyond PHP in future releases of the same rule. announced · Oct 2026 · source · release history
Automation Framework exit threshold configuration shipped Allows configuring the Automation Framework insights job to exit with a non-zero code only when findings meet or exceed a specified severity threshold, via the `exitAutoLevel` option.
Also counts toward: CI/CD pipeline integration
release
-
ZAP's Insights add-on (v0.7.0) adds an
exitAutoLeveloption (acceptingmediumorhigh) to the insights Automation Framework job, preferred over the now-secondaryexitAutoOnHighfield.
announced · Nov 2026
· source
· release history
example
-
Restrict a CI scan to exit non-zero only when high-severity findings exceed the threshold, using the new exitAutoLevel setting in the Insights Automation Framework job.
- type: insights parameters: exitAutoLevel: highannounced · Nov 2026 · source
Automation Framework Sites Tree Operations shipped Adds support for exporting the Sites Tree in text format for differential scans and pruning nodes from the Sites Tree via the Automation Framework.
Also counts toward: CI/CD pipeline integration
release
-
Adds
prunejob to the Automation Framework to remove nodes from the Sites Tree using a file in Sites Tree Format. 2.16.0 · Jan 2025 · source · release history - Adds standard Sites Tree Export feature, allowing export of the Sites Tree in a text format for differential scans in CI/CD. 2.16.0 · Jan 2025 · source · release history
LLM-driven Alert Confidence Review shipped Enables the use of an LLM to re-assess alert confidence levels within the Alert Filters workflow.
release
-
Adds an LLM-driven Review using LLM/AI action to Alert Filters for re-assessing alert confidence.
announced · Sep 2026
· source
· release history
LLM-driven OpenAPI Import shipped Leverages an LLM to assist in importing and processing OpenAPI specifications.
release
-
Adds an LLM-driven OpenAPI importer to the OpenAPI Support add-on.
announced · Sep 2026
· source
· release history
OpenAPI Import Request Sending shipped Adds the capability to send HTTP requests when importing a HAR file, including via the Automation Framework and API.
release
-
Adds an option to send requests when importing a HAR file in the Import/Export add-on, including via the Automation Framework and API.
announced · Sep 2026
· source
· release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
No command matches.
| option | found in | since | description |
|---|
Values are placeholders taken from each option’s declared default. Nothing is executed here — the output shown is a recording of a run that already happened.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
- Community health
-
Contributor trend distinct committers, this year against last
-
Maintainer concentration bus factor now against a year ago
-
Issue backlog trend issues closed per issue opened, 12 months
-
Responsiveness median time to a maintainer’s first reply
Nine scores for OWASP ZAP, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail OWASP ZAP puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Releases
13 entries
No entries match these filters.
- November 20262
- October 20263
- September 20262
- August 20262
- December 20251
- March 20251
- January 20252
Project health
Issue, contributor and maintainer activity in zaproxy/zaproxy, 2023-10 – 2026-09, as of 2026-09-25. Twelve-month figures first; the trend lines run the whole window.
- Contributors 21 +5 vs prior 12 months
- Maintainers 3 +0 joined · −0 left, last 12 months
- Bus factor 2 committers behind half the commits
- Community-filed 91% of issues opened, last 12 months
- Median time to close 17 days first maintainer reply 0.9 hours
- Open backlog 808 of 5,366 issues ever filed
- Issues opened / month 2 · 0 communitymaintainers
- Open backlog 808
- Contributors / month 4
- Commits / month 8
- Stars 15,771
- bugs 31%
- features 17%
- questions 2%
- docs 1%
- other 49%
Counts from the project's public repository and git history; no individuals are identified. Maintainers are the committers covering 80% of the last year's commits. how we measure this
Libraries its release ships
What its latest release locks, checked against known advisories.None of its release's images build from a lockfile we can read.
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →