Invicti
Release 20261028 (2026-10-28) commercialThe section your link pointed to isn't on Invicti's page any more, so we've brought you to the top.
Official documentation for Invicti AppSecAppSecApplication security: the practice of finding and fixing vulnerabilities in software during design, development, and testing. Cyber tools build on AppSec workflows to shift vulnerability detection earlier in the development lifecycle. Platform, Invicti Platform, and Invicti Enterprise — web application security testing, DASTDASTDynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces., API security, and vulnerability management.
GET /api/website-discovery
export INVICTI_MINIMUM_CONFIDENCE=confirmed
# INVICTI_MINIMUM_SEVERITY is intentionally not set
scan-cli scan --target-url https://app.example.com
export INVICTI_IGNORE_SSL_CHECKS=true
scan-cli scan --target-url https://app.internal.example.com
curl -X GET 'https://<invicti-host>/api/v1/clients?expand=credentials' \
  -H 'Authorization: Bearer <token>' \
  -H 'Accept: application/json'
export INVICTI_INCREMENTAL_SCAN=true && ./scan-cli -t https://api.example.com
INVICTI_INCREMENTAL_SCAN=true ./scan-cli --target https://api.example.com
GET /api/v1/vulnerabilities?severity=critical
POST /api/v1/targets/<id>/settings
{
  "max_scan_duration": 30
}
Summary
Invicti is a commercial web application security platform that runs dynamic and static scans against web apps, websites, and APIs to find and manage vulnerabilities. It's delivered as on-demand (cloud) or on-premises Platform and Enterprise editions, with scans executed through cloud or internal agents, making it suited to application security and DevSecOps teams who need scanning wired into CI/CD pipelines rather than run ad hoc from a laptop. Its documentation frames it around DAST and API testing with authentication handling, credential storage via Secrets Manager (including HashiCorp Vault), and gRPCgRPCAn open-source remote procedure call framework from Google that uses HTTP/2 and Protocol Buffers to let services call each other's functions across a network, giving tools low-latency, strongly typed inter-process communication. coverage, positioning it as a broader AppSec platform rather than a single-purpose scanner. Launched in 2009 and still shipping regularly, with 21 tracked releases and the most recent just 29 days ago, it shows active, ongoing development.
Official documentation for Invicti AppSec Platform, Invicti Platform, and Invicti Enterprise — web application security testing, DAST, API security, and vulnerability management.
How Invicti helps
Which of my web applications and APIs have exploitable vulnerabilities right now?
crawls and actively tests the running application or API and reports confirmed findings by severity, rather than relying on source review alone
Can my scanner get past login to test the pages that require authentication?
records a login sequence and replays it during scanning, with AI-assisted recovery when the recorded steps fail to reproduce a working session
Are the credentials my scans use to log in stored anywhere someone could read them?
pulls authentication secrets from a managed Secrets Manager, including retrieval directly from HashiCorp Vault, instead of holding them in scan configuration
Do my gRPC services get the same security testing as my REST APIs?
takes the service's Protobuf contract, including multiple proto files bundled together, and uses it to generate and run DAST checks against the gRPC endpoints
Did a finding I already triaged get flagged again in the next scan?
carries forward the Ignored or False Positive status assigned to a vulnerability into later scans instead of reporting it as new each time
Who changed the provisioning or scanning settings on this account, and when?
logs SCIM configuration changes and other administrative actions to an audit trail showing the user and timestamp behind each change
Languages
Features
Built from Invicti's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- Invicti covers 4 of the 8 vulnerability assessment methods capabilities we track.
What Invicti offers you
- CI/CD pipeline integration6
- CSV data export3
- REST API2
- Scheduled jobs2
- Self-hosted deployment2
- Administrative audit log1
- Agent-based deployment1
- Command-line interface1
- gRPC API support1
- JSON data export1
- Role-based access control1
- Ticketing integration1
- User-defined detection rules1
No capabilities match.
Web vulnerability scanning 22 features Vulnerability assessment methods since 2025
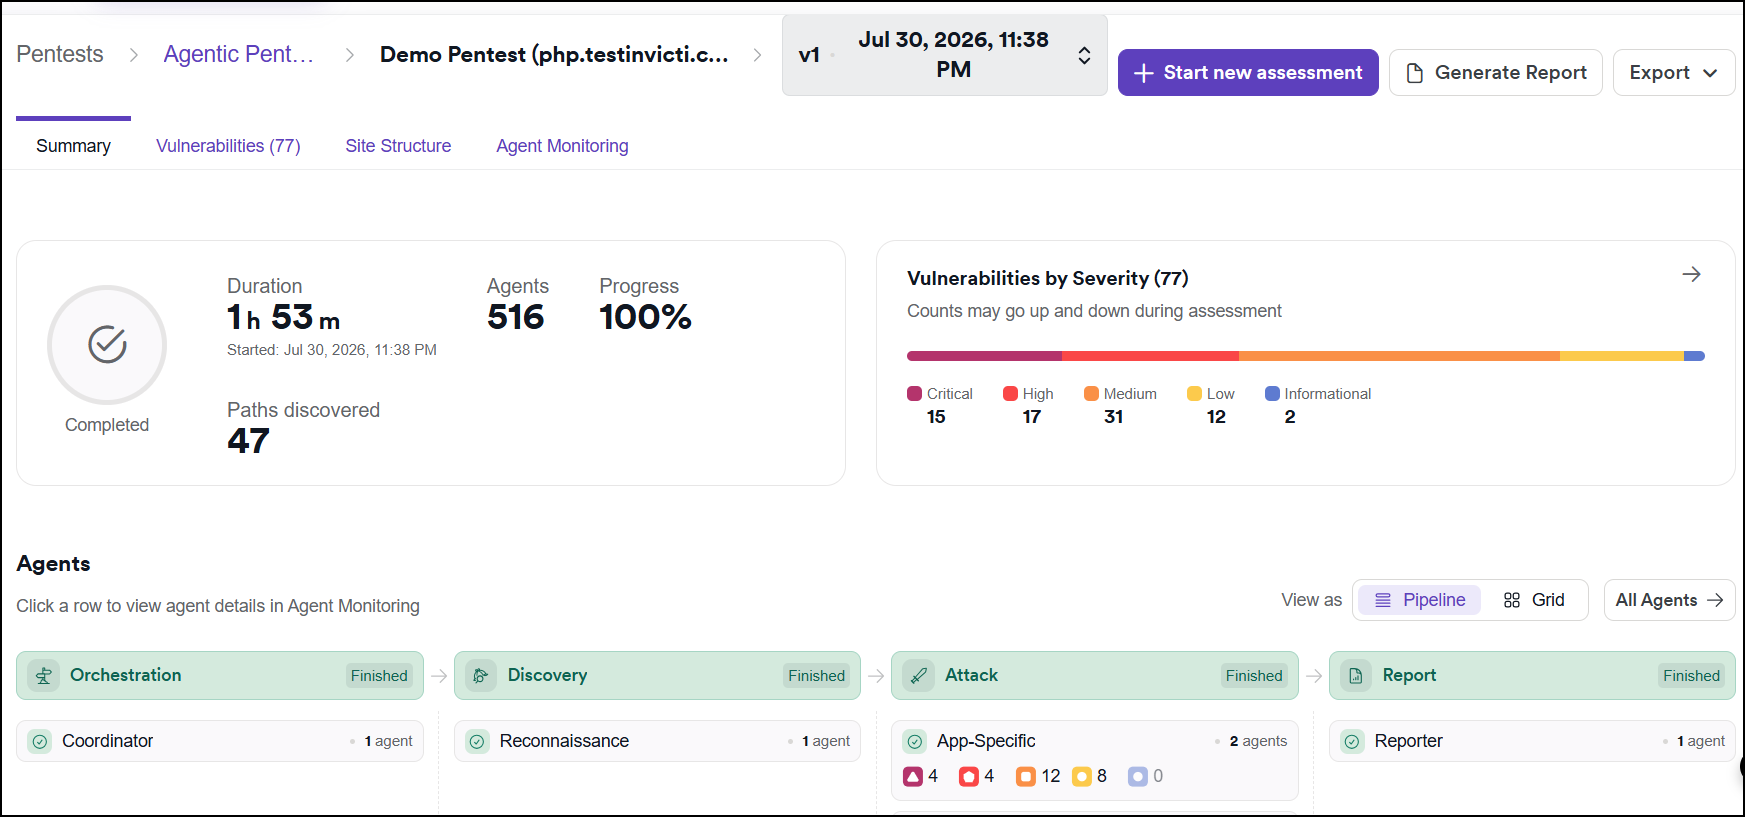
Agentic pentesting shipped Runs AI-driven attack agents against a target to discover vulnerabilities autonomously, with agents prioritizing relevant inputs, respecting scope and excluded paths, and expanding coverage to include Ruby deserialization, JWT bypass, and path-traversal techniques.
Shared capability: Web vulnerability scanning
release 35 total
-
Surfaces sitemap coverage for scan-wide agents at the specific sitemap path tested rather than the root.
 changelog · Oct 2026
· source
· release history
- Expands attack agent detection coverage to include Ruby deserialization vulnerabilities, additional JWT authentication bypass techniques, and path traversal that bypasses simple blocklist filters. changelog · Oct 2026 · source · release history
- Enforces scope boundaries via Octo blocking attack agent requests that fall outside target configuration and scope settings. changelog · Oct 2026 · source · release history
- Adds Agentic Pentests management directly from the platform UI, with findings flowing into the same pipeline as standard DAST scans for unified visibility and triage. changelog · Oct 2026 · source · release history
- Adds automatic false positive marking for DAST findings when agentic analysis confirms they are false positives. changelog · Oct 2026 · source · release history
- Enables the Recon agent to use documentation and diagrams inside uploaded source code archives (such as README files and architecture diagrams) to discover more attack surface. changelog · Oct 2026 · source · release history
docs
- Run AI-powered agentic pentests with Octo - create and launch assessments, manage them, and review findings, agent traces, and reports. seen Oct 2026 · source
- Agentic Pentesting: Release 20261001 Release date: 1 October 2026 note This release note applies to Invicti Agentic Pentesting, which requires a separate license. docs update · Oct 2026 · source
example
-
Visualize which endpoints and inputs were covered by the current agentic scan via the sitemap interface.
In the Assessment view, open the `sitemap` panel to inspect `path-level` and `input-level` coverage metrics.Agentic Pentesting: Release 20260831 · Aug 2026 · source
Scan CLI shipped Provides a command-line interface for triggering DAST scans, with automatic retry on temporary authentication errors and distinct error codes for rejected API tokens versus target or scan errors.
Shared capability: Web vulnerability scanning
Also counts toward: Command-line interface
release 14 total
-
Improves Scan CLI authentication error reporting to distinguish credential rejections from target errors
 Release 20261001 · Oct 2026
· source
· release history
- Scan CLI now distinguishes a rejected API token as a credential error, separate from target or scan errors. Release 20261001 (2026-10-01) · Oct 2026 · source · release history
- Enables automatic retry for temporary authentication errors in Scan CLI Release 20261001 · Oct 2026 · source · release history
- Scan CLI now automatically retries requests that receive a temporary authentication error. Release 20261001 (2026-10-01) · Oct 2026 · source · release history
-
The
INVICTI_IGNORE_SSL_CHECKSenvironment variable in scan-cli now applies to all outbound platform API calls made during a scan — including DAST, Inventory, Identity, and report/export endpoints — not just the ephemeral agent.
changelog · Sep 2026
· source
· release history
-
The
INVICTI_MINIMUM_CONFIDENCEenvironment variable in scan-cli now independently fails a scan when its threshold is exceeded, without also requiringINVICTI_MINIMUM_SEVERITYto be set. changelog · Sep 2026 · source · release history
example
-
Allow scan-cli to reach an Invicti platform instance behind a self-signed TLS certificate, ensuring all API calls (DAST, Inventory, Identity, report/export) bypass SSL verification.
export INVICTI_IGNORE_SSL_CHECKS=true scan-cli scan --target-url https://app.internal.example.comchangelog · Sep 2026 · source
gRPC service scanning shipped Scans gRPC-based APIs by accepting Protobuf definition files at scan setup time.
Shared capability: Web vulnerability scanning
Also counts toward: gRPC API support
release 8 total
-
Adds gRPC compatibility by sending the
trailersheader and an empty gRPC frame for parameterless RPCs.
changelog · Oct 2026
· source
· release history
- Adds clearer messaging about maximum file size limits for API source uploads. changelog · Oct 2026 · source · release history
- Adds support for uploading multiple gRPC proto file definitions as a single ZIP archive, eliminating one-by-one imports for multi-file services. changelog · Aug 2026 · source · release history
- Adds the ability to upload multiple gRPC proto file definitions as a single ZIP archive for scanning. Release 20260806 (2026-08-06) · Aug 2026 · source · release history
- Supports uploading multiple gRPC proto file definitions as a single ZIP archive for gRPC scanning, removing the need to import proto files one by one for services that span multiple files. Release 20260806 (2026-08-06) · Aug 2026 · source · release history
-
gRPCscanning now accepts multiple.protofile definitions packed into a singleZIParchive Release 20260806 · Aug 2026 · source · release history
docs
- Release 20260806 Release date: 6 August 2026 Multiple proto files as a ZIP archive for gRPC scanning: You can now upload multiple gRPC proto file definitions as a single ZIP archive, making it easier to scan services that span multiple proto files without importing them one by one. docs update · Aug 2026 · source
example
-
Scan a gRPC service split across many .proto files without importing them individually.
Upload the combined proto_definitions.zip via the new scanning upload interface.Release 20260806 (2026-08-06) · Aug 2026 · source -
Scan gRPC-based APIs by providing their protocol buffer definitions directly to the scanner.
Upload `.proto` files via the New Scan wizard's service configuration panelRelease 20260625 (2026-06-25) · Jun 2026 · source -
Add gRPC DAST coverage to a microservice by supplying its Protobuf contract at scan configuration time.
In the Invicti console, go to New Scan > API Scanning, select gRPC as the API type, and upload the service's .proto definition file before launching the scan.Release 20260625 (2026-06-25) · Jun 2026 · source
CI/CD pipeline integration shipped Connects DAST scanning directly into CI/CD pipelines so security checks run as part of the build process.
Shared capability: Web vulnerability scanning
Also counts toward: CI/CD pipeline integration
release 7 total
-
Leaving the minimum severity field empty in the CI/CD script generator now produces a script with no minimum vulnerability threshold, applying to Azure Pipelines, CircleCI, GitHub Actions, GitLab CI/CD, and Jenkins.
changelog · Sep 2026
· source
· release history
- Adds a direct link to the Invicti Azure Marketplace plugin in the Azure Pipelines CI/CD integration setup screen Release 20260723 (2026-07-23) · Jul 2026 · source · release history
- Adds a direct link to the Invicti Azure Pipelines plugin in the Azure Marketplace within the CI/CD integration setup, enabling plugin-based integration alongside the existing script-based method. Release 20260723 (2026-07-23) · Jul 2026 · source · release history
- Includes a direct link to the Invicti plugin in Azure Marketplace for Azure Pipelines CI/CD integration Release 20260723 · Jul 2026 · source · release history
- Implements automatic DAST scans in the GitHub Actions CI/CD pipeline Release 20250911 · Sep 2025 · source · release history
- Makes Scan Profiles required for all CI/CD integrations Release 20250911 · Sep 2025 · source · release history
example
-
Generate a CI/CD script in GitHub Actions with no minimum severity gate, so the pipeline reports all findings without blocking on severity.
In the Invicti platform, go to Integrations > CI/CD Script Generator, select 'GitHub Actions', leave the 'Minimum Severity' field empty, and download the generated script.changelog · Sep 2026 · source -
Fail a CI pipeline when scan confidence exceeds a threshold, without also gating on severity — useful when you want confidence-only quality gates.
export INVICTI_MINIMUM_CONFIDENCE=confirmed # INVICTI_MINIMUM_SEVERITY is intentionally not set scan-cli scan --target-url https://app.example.comchangelog · Sep 2026 · source
Application and Collection Scan Scheduling shipped Allows administrators to create scan schedules for entire applications or collections, automatically running DAST scans across all included targets on a chosen recurrence.
Shared capability: Web vulnerability scanning
Also counts toward: Scheduled jobs
release
-
Adds the ability to create scan schedules for an entire application or collection, automatically running DAST scans across all included targets on a chosen recurrence.
changelog · Sep 2026
· source
· release history
- Adds scheduled scans for entire applications or collections, automatically running DAST scans across all included targets on a chosen recurrence (previously schedules were per-target only). changelog · Aug 2026 · source · release history
- Adds App-level and Collection-level Scheduled Scans for DAST runs across all included targets Release 20260820 · Aug 2026 · source · release history
- Scan schedules now support deleting the scans they created upon schedule deletion via Delete scans created by a schedule Release 20260514 (2026-05-14) · May 2026 · source · release history
- Adds safeguards to automatically pause recurring scans after five consecutive failures Release 20260122 · Jan 2026 · source · release history
docs
- Release 20260820 Release date: 20 August 2026 Scheduled scans for applications and collections: You can now create scan schedules for an entire application or collection, automatically running DAST scans across all included targets on your chosen recurrence. changelog · Aug 2026 · source
example
-
Create a recurring DAST scan schedule across an entire application or collection without manual intervention.
steps: Navigate to the Application or Collection, open Schedules, and create a new recurrence rule for all included targets.Release 20260820 · Aug 2026 · source -
Assign a descriptive name to a recurring scan for easier identification in the dashboard.
In the Scheduling interface, enter your desired label in the 'Custom Name' field before saving.Release 20260205 (2026-02-05) · Feb 2026 · source
Rate-Limit Aware Scan Pacing shipped Automatically throttles request timing and applies exponential backoff with jitter when targets respond with rate-limit headers or 429 status codes to improve crawl coverage.
Shared capability: Web vulnerability scanning
release
-
The scan engine now applies exponential backoff with jitter when retrying requests that receive a
429 Too Many Requestsresponse with no Retry-After header.
changelog · Sep 2026
· source
· release history
-
The scan engine now automatically throttles request pacing when it receives Retry-After or
X-RateLimit-*rate-limiting response headers, reducing incomplete coverage and false-negative findings. changelog · Sep 2026 · source · release history -
Introduces rate-limit-aware scan pacing: the scan engine now automatically throttles request timing when it receives Retry-After or
X-RateLimit-*response headers, reducing incomplete coverage on rate-limited targets. Release 20260903 (2026-09-03) · Sep 2026 · source · release history -
Implements rate-limit-aware scan pacing: the scan engine automatically throttles request pacing when it receives Retry-After and
X-RateLimit-*response headers Release 20260903 (2026-09-03) · Sep 2026 · source · release history -
Scan engine automatically throttles request pacing on Retry-After and
X-RateLimit-*response headers for rate-limit-aware scanning Release 20260903 · Sep 2026 · source · release history - Scan engine now applies exponential backoff with jitter when retrying requests that receive a 429 Too Many Requests response with no Retry-After header, improving crawl coverage on rate-limited targets. changelog · Aug 2026 · source · release history
API scan profiles shipped Applies appropriate scan profiles to API targets rather than restricting them to a single preset.
Shared capability: Web vulnerability scanning
release
-
Adds a new dedicated API scan profile applied by default to all new API targets for comprehensive API vulnerability coverage.
changelog · Aug 2026
· source
· release history
- New dedicated API scan profile applied by default to all new API targets for comprehensive API vulnerability coverage. Release 20260709 (2026-07-09) · Jul 2026 · source · release history
- New API scan profile is now the default for all new API targets, providing comprehensive API vulnerability coverage. Release 20260709 · Jul 2026 · source · release history
-
api_scan_profile: A new scan profile designed specifically for APIs, now applied by default to all new API targets for comprehensive coverage. Release 20260709 (2026-07-09) · Jul 2026 · source · release history - All scan profiles are now selectable for API targets — no longer locked to OWASP Top 10 API. Release 20260709 (2026-07-09) · Jul 2026 · source · release history
- Screenshot capture is now enabled during DAST scans to improve visibility of the scanning process and authentication failures. Release 20260205 (2026-02-05) · Feb 2026 · source · release history
Scan Location Export Enhancements shipped Extends scan location exports in CSV, JSON, and XML formats to include HTTP methods and status codes for verifying crawl coverage and spotting authentication gaps.
Shared capability: Web vulnerability scanning
Also counts toward: CSV data export, JSON data export
release
-
Adds HTTP Methods and Status Codes columns to CSV (Locations) scan location exports, appended at the end of each row.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
changelog · Sep 2026
· source
· release history
- Adds HTTP method and HTTP response code fields to JSON and XML scan location export formats. changelog · Sep 2026 · source · release history
docs
- HTTP method and status code in scan location exports: The CSV (Locations), JSON, and XML export formats now include the HTTP method and HTTP response code for each crawled URL, so you can quickly verify scan coverage and spot authentication gaps such as 401 or 403 responses on specific routes. docs update · Sep 2026 · source
example
-
After a scan completes, export locations in CSV to spot routes returning 401 or 403 — indicating authentication gaps in crawl coverage.
In the scan results, go to Scan > Locations > Export, select 'CSV (Locations)', then open the file and filter the 'Status Codes' column for 401 or 403 responses.changelog · Sep 2026 · source
Custom scan speed control shipped Lets users set request concurrency and frequency to avoid overloading sensitive targets during a scan.
Shared capability: Web vulnerability scanning
release
-
Adds a new Custom scan speed option in scan configuration to set the number of concurrent requests and throttling delay for precise throughput control.
changelog · Aug 2026
· source
· release history
- New Custom scan speed option lets you set the number of concurrent requests and send frequency for precise scan throughput control. Release 20260709 (2026-07-09) · Jul 2026 · source · release history
-
custom_scan_speed: New scan configuration option allowing precise control over the number of concurrent requests and request frequency for throughput management. Release 20260709 (2026-07-09) · Jul 2026 · source · release history
example
-
Tune scan throughput for a sensitive target without triggering rate-limiting or WAF blocks.
In the scan configuration, open Scan Speed and select Custom, then set the number of concurrent requests and the request send frequency to values appropriate for your target environment.Release 20260709 (2026-07-09) · Jul 2026 · source
Time-based vulnerability confirmation shipped Confirms time-based findings by running multiple rounds with varied delay values and including per-round timing evidence in reports, reducing false positives from network latency or server load.
Shared capability: Web vulnerability scanning
release
-
Octo now confirms time-based findings over multiple rounds with varied delay values to reduce false positives from network latency or server load.
changelog · Oct 2026
· source
· release history
-
Validate time-based findings over multiple rounds with varied delay values to reduce false positives from network latency or server load
Release 20261001 (2026-10-01) · Oct 2026
· source
· release history
- Time-based vulnerability confirmation now runs multiple rounds with varied delay values, including per-round timing evidence in finding reports. Release 20261001 (2026-10-01) · Oct 2026 · source · release history
Ephemeral API Targets shipped Supports dynamic base URLs that resolve at scan time, enabling the scanning of temporary or CI/CD-provisioned environments without manual target reconfiguration.
Shared capability: Web vulnerability scanning
Also counts toward: CI/CD pipeline integration
release
-
Adds ephemeral API targets with a dynamic base URL that resolves at scan time, enabling scanning of temporary or CI/CD-provisioned environments without manual target reconfiguration.
changelog · Aug 2026
· source
· release history
- Introduces support for Ephemeral API targets with a dynamic base URL that resolves at scan time Release 20260820 (2026-08-20) · Aug 2026 · source · release history
example
-
Use dynamic base URLs for ephemeral API environments that are provisioned during CI/CD.
steps: Go to API Targets > New Target > Select 'Ephemeral' type, then set the Dynamic Base URL field.Release 20260820 · Aug 2026 · source
Interactive login for scans shipped Allows a human operator to manually complete CAPTCHA or MFA challenges during a scan, reducing authentication-related scan failures, now supported on internal agents as well as cloud agents.
Shared capability: Web vulnerability scanning
release
- Interactive login (manual CAPTCHA/MFA completion) is now available for scans run through internal agents, not just cloud agents. Release 20260625 (2026-06-25) · Jun 2026 · source · release history
-
Adds
interactive loginconfiguration for DAST scans to allow manual CAPTCHA/MFA completion Release 20260430 (2026-04-30) · Apr 2026 · source · release history
example
-
Reduce scan failures on sites with CAPTCHA or MFA when scanning through an internal agent by enabling interactive login.
In the scan profile settings for an internal agent scan, enable the AI-aided Login setting so Invicti can use AI to recover failed Login Sequence Recorder playbacks automatically.Release 20260625 (2026-06-25) · Jun 2026 · source
Scan profile cloning shipped Allows scan profiles to be cloned to different targets, enabling configuration reuse across multiple websites without manual setup.
Shared capability: Web vulnerability scanning
release
- Added an ability to copy custom scan profiles Release 20251023 · Oct 2025 · source · release history
docs
- Release v26.10.0 Release date: 8 October 2026 Clone scan profiles to different targets: Added the ability to clone scan profiles to different targets, allowing you to reuse configurations across multiple websites without manual setup. seen Oct 2026 · source
- Release v26.10.0 Release date: 8 October 2026 Clone scan profiles to different targets: Added the ability to clone scan profiles to different targets, allowing you to reuse configurations across multiple websites without manual setup. seen Oct 2026 · source
Screenshot Capture During Scans shipped Enables automatic screenshot capture during DAST scans to provide visibility into the scanning process and authentication failures.
Shared capability: Web vulnerability scanning
release
- Captures screenshots during DAST scans to improve visibility of authentication failures and scanning progress Release 20260205 · Feb 2026 · source · release history
- Screenshot capture is now enabled during DAST scans to improve visibility of the scanning process and authentication failures. Release 20260205 (2026-02-05) · Feb 2026 · source · release history
API-only scanning shipped Allows users to configure scans that target only API endpoints, improving speed and efficiency by ignoring non-API web assets.
Shared capability: Web vulnerability scanning
release
- Implemented API-only scan capability to improve scan speed and efficiency Release 20251023 · Oct 2025 · source · release history
example
-
Scan only API endpoints to reduce noise and improve speed compared to a full web app scan.
In the scan profile, enable 'API-only' capability for the target URL.Release 20251023 · Oct 2025 · source
HTTP method targeting shipped Allows scans to be restricted to specific HTTP methods (such as GET or POST) for API or web targets to reduce noise and improve speed.
Shared capability: Web vulnerability scanning
release
- DAST scan targets can now be restricted to specific HTTP methods during configuration Release 20250814 · Aug 2025 · source · release history
example
-
Restrict a DAST scan to only test GET and POST methods on a target URL
Steps: In the Invicti UI, navigate to Scan Configuration > Target Settings and enable 'HTTP Methods', then select 'GET' and 'POST'.Release 20250814 · Aug 2025 · source
SSRF vulnerability testing shipped Tests targets for SSRF vulnerabilities via an SSRF responder that registers during scans to detect server-side request forgery issues.
Shared capability: Web vulnerability scanning
release
- Introduces LLM vulnerability detection capabilities including Command Injection, SSRF, Insecure Output Handling, Tool Usage Exposure, Prompt Injection, System Prompt Leakage, and Fingerprinting. Release 20250730 · Jul 2025 · source · release history
docs
-
Release v26.10.0 Release date: 8 October 2026 SSRF responder registration: Fixed an issue that prevented the SSRF responder from registering, ensuring that security scans can successfully test for SSRF vulnerabilities.
 seen Oct 2026
· source
OCTO Sitemap Exclusion Capabilities shipped Adds the ability to exclude specific URL paths and parameters in the OCTO sitemap, aligning it with DAST scan exclusion capabilities.
Shared capability: Web vulnerability scanning
release
-
Adds the ability to exclude URL paths and parameters in the OCTO sitemap, bringing it in line with DAST scan exclusion capabilities.
changelog · Sep 2026
· source
· release history
Custom Security Checks Support documented Allows users to create and run custom security checks in on-premises deployments to extend DAST scan coverage for specific environment requirements.
Shared capability: Web vulnerability scanning
Also counts toward: User-defined detection rules, Self-hosted deployment
docs
-
Release 26.243.260831140137 Helm chart: 26.243.260831140137 Windows installer: 26.9.2.1328 Release date: 1 September 2026 Custom Security Checks: You can now create and run custom security checks in your on-premises deployment, extending DAST scan coverage with checks designed for your specific environment and…
 docs update · Sep 2026
· source
API-Only Scan Scope Restriction shipped Restricts API-only scans to imported API specification files only, disabling probes to other endpoints to reduce noise.
Shared capability: Web vulnerability scanning
release
- API-only scans are now restricted to imported API specification files only; probes to other endpoints are no longer performed Release 20260611 (2026-06-11) · Jun 2026 · source · release history
Custom User Agent support shipped Allows configuration of a custom User Agent string in scan profiles to mimic specific clients or bypass restrictions.
Shared capability: Web vulnerability scanning
release
- Displays the custom User Agent option in Scan Configuration for Targets Release 20250911 · Sep 2025 · source · release history
Advanced scan configuration per target documented Configures advanced scan behaviour for individual targets, including scan auto-tuning, element exclusions, and parameter exclusions.
Shared capability: Web vulnerability scanning
docs
- Configure advanced scan behavior for a target, including scan auto-tuning, element exclusions, and parameter exclusions. seen Oct 2026 · source
Credentialed vulnerability scanning 4 features Vulnerability assessment methods since 2025
Secrets Manager shipped Stores scan credentials centrally, including support for HashiCorp Vault and client certificates, accessible from within the Login Sequence Recorder.
Shared capability: Credentialed vulnerability scanning
release 14 total
-
Store client certificate files as secrets and select them in a target's client certificate authentication settings.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Release 20261028 (2026-10-28) · Oct 2026
· source
· release history
-
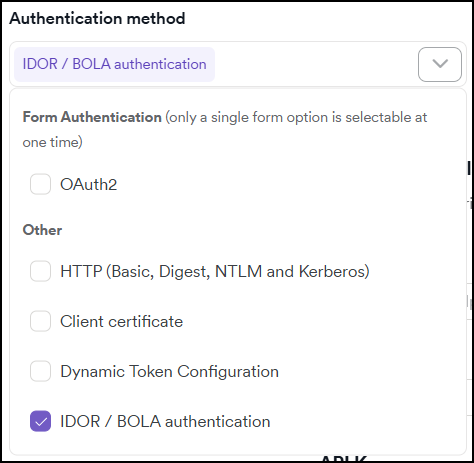
Secrets Manager credentials for IDOR/BOLA authentication support API key, basic auth, and bearer token credential types
Release 20260903 · Sep 2026
· source
· release history
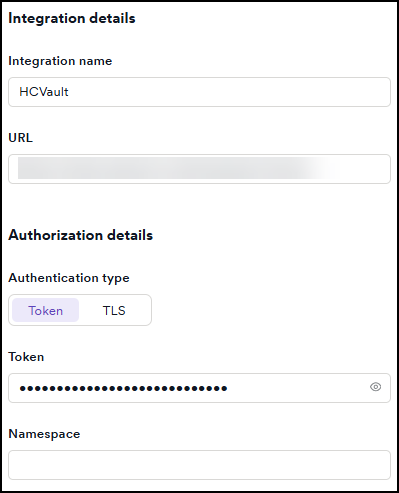
- Adds HashiCorp Vault integration with Invicti Platform's Secrets Manager, enabling credentials to be retrieved directly from Vault when configuring scan authentication. changelog · Aug 2026 · source · release history
- New HashiCorp Vault integration: Secrets Manager can now retrieve credentials directly from HashiCorp Vault for scan authentication. Release 20260709 (2026-07-09) · Jul 2026 · source · release history
-
client_cert_secrets_manager: Ability to store client certificates in base64 format within Secrets Manager for use in scan credentials. Release 20260709 (2026-07-09) · Jul 2026 · source · release history -
hashicorp_vault_integration: Connect the Secrets Manager to HashiCorp Vault to retrieve credentials directly during scan authentication configuration. Release 20260709 (2026-07-09) · Jul 2026 · source · release history
example
-
Configure a target to use Secrets Manager for all credential fields instead of just simple form auth.
Reference 'Secrets Manager' credentials in every field when configuring a TargetRelease 20260514 (2026-05-14) · May 2026 · source
Login Sequence Recorder (LSR) shipped Records and replays login sequences so the scanner can authenticate before testing protected pages.
Shared capability: Credentialed vulnerability scanning
release 12 total
-
Adds HAR file export from login sequence recording sessions, with sensitive headers masked, to assist Support troubleshooting.
Release 20261015 (2026-10-15) · Oct 2026
· source
· release history
- Adds specific failure messages when login sequence playback, session recovery, or automatic login fails, replacing generic errors. Release 20261015 (2026-10-15) · Oct 2026 · source · release history
- Blends secret values in login sequence and business logic recording UI to hide sensitive data during capture Release 20261001 · Oct 2026 · source · release history
-
Expands Login Sequence Recorder (LSR) reports to include the full HTTP request and response for each recorded step, with automatic obfuscation of sensitive tokens in headers and bodies.
changelog · Aug 2026
· source
· release history
- Secrets configured for a target are now accessible to the Login Sequence Recorder (LSR) during recording, so stored credentials can be used instead of entering them manually. changelog · Aug 2026 · source · release history
- Adds full HTTP request and response data to Login Sequence Recorder (LSR) reports, with automatic obfuscation of sensitive tokens in headers and bodies Release 20260723 (2026-07-23) · Jul 2026 · source · release history
docs
- Release 20260723 Release date: 23 July 2026 HTTP request and response details in LSR reports: Login Sequence Recorder (LSR) reports now include the full HTTP request and response for each recorded step, so you can review the exact traffic your login sequence generates. docs update · Jul 2026 · source
example
-
Configure LSR with authentication scripts for advanced login flows
Upload authentication script to Standalone LSR configuration in the Invicti UIRelease 20251009 · Oct 2025 · source
Scan termination on authentication failure shipped Configures scans to immediately fail and flag incomplete results when authentication problems occur, preventing false-clean outcomes.
Shared capability: Credentialed vulnerability scanning
Also counts toward: CI/CD pipeline integration
release
-
Adds a scan failure mode triggered by authentication problems, so scans that never ran authenticated are flagged rather than silently returning incomplete results.
changelog · Oct 2026
· source
· release history
example
-
Fail a pipeline stage immediately when a scan runs without successful authentication, preventing false-clean results.
In the scan policy or scan settings, enable the option to fail a scan on authentication issues so the scan reports failure instead of returning unauthenticated results.changelog · Oct 2026 · source
Secrets in Custom Authentication Scripts documented Adds support for using stored secrets within custom authentication scripts, allowing secure management of sensitive credentials during automated scans.
Shared capability: Credentialed vulnerability scanning
docs
- Release v26.9.1 Release date: 24 September 2026 Secrets in custom authentication scripts: Added support for secrets in custom authentication scripts, allowing you to securely manage and test sensitive credentials during automated scans. docs update · Sep 2026 · source
Vulnerability database matching 1 feature Vulnerability assessment methods since 2026
Vulnerability database (VDB) updates documented Keeps the vulnerability database current so scans check for the latest known issues.
Shared capability: Vulnerability database matching
docs
- Release 20260928 Release date: 28 September 2026 Updated the vulnerability database (VDB) to version 20260922 Updated severity ratings for Artifactory versions 7.161.15, 7.161.16 from Information to Low Updated severity rating for Ruby version 1.9.0 from High to Critical Updated severity ratings for TornadoWebServer… seen Oct 2026 · source
- Release 20261001 Release date: 7 October 2026 Updated the vulnerability database (VDB) to version 20261001 Updated severity rating for Dolibarr version 23.0.4 from Low to Medium CVE-2026-101898 CVE-2026-101900 CVE-2026-101901 CVE-2026-101902 CVE-2026-101903 CVE-2026-101904 CVE-2026-101905 CVE-2026-101906… seen Oct 2026 · source
- Release v26.7.1 Release date: 28 July 2026 Agents page now alerts you when vulnerability database updates can't be completed: Added a notification to the agents page that alerts you when vulnerability database updates fail due to connection issues, with guidance on how to resolve the issue. docs update · Jul 2026 · source
- Release 20260723 Release date: 23 July 2026 Updated the vulnerability database (VDB) to versions 20260714 and 20260717 (hotfix) Updated severity ratings for Angular versions 0.9.0–0.9.7, 0.9.9–0.9.19, 0.10.0–0.10.6, 1.0.0–1.0.8, 1.1.0–1.1.5, 1.2.0–1.2.32, 2.0.0–2.0.2, 2.1.0–2.1.2, 2.2.0–2.2.4, 2.3.0–2.3.1,… docs update · Jul 2026 · source
- 26.7.1 26.7.1 Release v26.7.1 Release date: 28 July 2026 Agents page now alerts you when vulnerability database updates can't be completed: Added a notification to the agents page that alerts you when vulnerability database updates fail due to connection issues, with guidance on how to resolve the issue. docs update · Jul 2026 · source
Static application security testing 1 feature Vulnerability assessment methods since 2025
SAST source metadata visibility shipped Displays last updated timestamps and modification history for SAST sources to aid in audit and configuration management.
Shared capability: Static application security testing
release
- SAST sources in Projects now display a Last updated timestamp per source Release 20250814 · Aug 2025 · source · release history
Other / not yet classified 62 features Features we have not matched to a capability yet. A suggested match is marked.
Assessment diagnostics and reporting shipped Allows users to download scanner logs and raw agent traces as a compressed archive, and to export assessment reports in HTML format for stakeholder sharing or browser viewing.
release 12 total
-
Enables HTML format download for assessment reports, ready to open in any browser or share with stakeholders.
changelog · Oct 2026
· source
· release history
- Enables download of scanner logs and raw agent traces as a single compressed archive per assessment. changelog · Oct 2026 · source · release history
-
Download scanner logs and raw agent traces as a single compressed archive for detailed investigation or support cases
Release 20261001 (2026-10-01) · Oct 2026
· source
· release history
- Enables downloading scanner logs and raw agent traces as a single compressed archive per assessment. Release 20261001 (2026-10-01) · Oct 2026 · source · release history
- Enables downloading assessment reports in HTML format for browser viewing or stakeholder sharing. Release 20261001 (2026-10-01) · Oct 2026 · source · release history
- Download assessment reports in HTML format via the UI for offline review or stakeholder sharing Release 20261001 (2026-10-01) · Oct 2026 · source · release history
example 8 total
-
Export an assessment report in HTML format to share findings with stakeholders who do not have platform access.
In the platform UI, open the assessment and select the HTML report download option to get a self-contained file ready to open in any browser.changelog · Oct 2026 · source -
Download scanner logs and agent traces after an assessment to share raw evidence with Invicti Support or investigate findings offline.
In the platform UI, open the assessment, then download the scanner logs and agent traces as a single compressed archive from the assessment detail view.changelog · Oct 2026 · source -
Share a self-contained assessment report with a stakeholder who does not have platform access.
In the Invicti platform, open the assessment and choose the HTML report download option to produce a file openable in any browser.changelog · Oct 2026 · source -
Download scanner logs and agent traces after an agentic pentest to investigate a finding in depth or escalate to Invicti Support.
In the Invicti platform, open the completed assessment, then select the option to download scanner logs and agent traces as a single compressed archive.changelog · Oct 2026 · source -
Download raw scanner logs and agent traces after an assessment to investigate a finding or share diagnostics with Invicti Support.
In the Invicti Platform, open the completed assessment, then select the option to download the scanner logs and agent traces as a single compressed archive.Release 20261001 (2026-10-01) · Oct 2026 · source -
Download investigation artifacts (logs and traces) for a specific assessment to share with support.
In the assessment details view, select 'Download' > 'Scanner logs and agent traces'.Release 20261001 (2026-10-01) · Oct 2026 · source
Sensorless API Discovery shipped suggested Automatically discovers APIs across the application, including those found on sites outside the defined scan scope.
Suggested capability: Web vulnerability scanning. This is our guess, not confirmed.
release 18 total
-
Adds target name and URL display and filtering, plus per-source discovery icons and a discovery-source column, to the API catalog so each API's origin is immediately visible.
changelog · Oct 2026
· source
· release history
-
Adds a setting to fail a scan when authentication problems occur, preventing unauthenticated results from being silently accepted.
Release 20261015 (2026-10-15) · Oct 2026
· source
· release history
- Adds discovery date filtering, exact-match and exclusion text filters, and multi-select risk score filtering to the Website Discovery list. changelog · Sep 2026 · source · release history
- Exposes Website Discovery via the Invicti Platform REST API, enabling retrieval of discovered websites and integration of discovery results into external workflows and cyber tooling.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ changelog · Sep 2026 · source · release history
- Improves Website Discovery count filtering: clicking a number in the list filters entries matching that value without leaving the page Release 20260917 · Sep 2026 · source · release history
- Adds a Website Discovery REST API endpoint to retrieve discovered websites and integrate discovery results into external workflows and cyber tooling.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Release 20260917 (2026-09-17) · Sep 2026 · source · release history
IDOR/BOLA scan credentials shipped suggested Stores the two sets of credentials needed to test for broken object-level authorisation vulnerabilities such as IDOR and BOLA.
Suggested capability: Credentialed vulnerability scanning. This is our guess, not confirmed.
release 14 total
-
Adds Bearer Token and API Key as dedicated, first-class authentication header types in target configuration, separate from functional headers, for easier authenticated scan setup.
changelog · Sep 2026
· source
· release history
- The character limit for authentication values in IDOR/BOLA credentials has been increased from 1,024 to 4,096 characters. changelog · Sep 2026 · source · release history
- Adds support for using Invicti Secrets Manager credentials (API key, basic auth, and bearer token types) for IDOR/BOLA authentication. changelog · Sep 2026 · source · release history
- Enables use of Invicti Secrets Manager credentials (API key, basic auth, bearer token) for IDOR/BOLA authentication configurations. Release 20260903 (2026-09-03) · Sep 2026 · source · release history
- Bearer Token and API Key are now dedicated first-class authentication header types in target configuration, separate from functional headers Release 20260903 · Sep 2026 · source · release history
- Introduces dedicated Bearer Token and API Key as first-class authentication header types in target configuration, separate from functional headers Release 20260903 (2026-09-03) · Sep 2026 · source · release history
example
-
Verify your API scanner can now handle token rotation without interruption during long-running assessments.
Configure the scan target to use dynamic/rotating tokens in the scan setup wizard.Release 20260330 · Mar 2026 · source
AI credit management shipped Tracks, displays, and manages AI credits consumed by agentic pentests, including a transaction ledger, real-time per-assessment usage, whole-number credit values, end-of-term expiry, and a pending/committed balance view before starting a new assessment.
release 10 total
-
Adds real-time credit usage display in the Summary tab for each assessment, reflecting consumed credits as the run progresses.
changelog · Oct 2026
· source
· release history
- Unused credits now expire at the end of your subscription term. changelog · Oct 2026 · source · release history
- Credit values are now whole numbers instead of decimal values, which may affect any integrations or displays that expected decimal credit balances. changelog · Oct 2026 · source · release history
- Assessment confirmation dialog now references the AI Services Addendum. changelog · Oct 2026 · source · release history
-
Adds real-time credit consumption to the Summary tab, showing credits used per assessment, with zero credit charge for failed assessments and pro-rated charges for canceled ones.
Release 20261001 (2026-10-01) · Oct 2026
· source
· release history
- Credit values are now expressed as whole numbers instead of decimals. Release 20261001 (2026-10-01) · Oct 2026 · source · release history
example
-
Review every credit addition, deduction, and pending reservation after kicking off an agentic pentest to track budget in real time.
In the platform UI, go to Pentests > AI Credit Usage to see the full transaction ledger, current balance, and any credits pending against running assessments.changelog · Oct 2026 · source -
Track how many AI credits each agentic pentest is consuming in real time — useful during a live assessment to stay within budget.
In the Invicti platform, go to Pentests > AI Credit Usage to review the full credit transaction ledger, then open an active assessment and select the Summary tab to see per-assessment credit…changelog · Oct 2026 · source -
Review pending and committed AI credits before starting a new agentic pentest to ensure sufficient balance.
In the Invicti Platform, go to Pentests > AI Credit Usage to view the full transaction ledger, including pending reservations for in-progress assessments and your current available balance.Release 20261001 (2026-10-01) · Oct 2026 · source -
Check remaining Agentic Pentesting credits and see what is currently committed to an active assessment.
Navigate to 'Pentests' > 'AI Credit Usage' in the main navigation bar.Release 20261001 (2026-10-01) · Oct 2026 · source
Vulnerability filtering by scope shipped Enables filtering of vulnerabilities and scan results by environment, application, asset, tags, or severity levels.
Also counts toward: REST API
release
-
Adds
collectionfilter on the Vulnerabilities page to scope results to specific collections alongside existing filters Release 20260611 (2026-06-11) · Jun 2026 · source · release history - Adds a Business Criticality filter and Business Impact column in the DAST vulnerabilities list to focus on high-value targets Release 20260528 · May 2026 · source · release history
- New Business Criticality filter and Business Impact column in the DAST vulnerabilities list view. Release 20260528 (2026-05-28) · May 2026 · source · release history
- Scan profiles now show the highest severity level reported by each check and support filtering checks by severity Release 20260402 · Apr 2026 · source · release history
-
GET /api/scans/resultsnow supports filtering scan results by tags Release 20251009 · Oct 2025 · source · release history -
Vulnerabilities page supports filtering by
application,asset, andenvironmentRelease 20250814 · Aug 2025 · source · release history
example
-
Filter vulnerabilities by a specific collection (e.g., Customer-Facing) on the Vulnerabilities page
In the UI, go to Vulnerabilities > Filters > Collection and select your target collectionRelease 20260611 (2026-06-11) · Jun 2026 · source -
Narrow your vulnerability list to findings belonging to a specific collection in the Invicti UI.
In the console, go to Vulnerabilities and use the Collection filter dropdown.Release 20260611 · Jun 2026 · source -
Filter the vulnerabilities dashboard to show only high-priority issues from business-critical assets.
Go to DAST > Vulnerabilities. In the filter sidebar, select 'Business Criticality' and choose the desired level (e.g., 'Critical').Release 20260528 · May 2026 · source -
Filter scan results by tags using the API
curl -X GET 'https://<invicti-url>/api/scans/results?tags=production'Release 20251009 · Oct 2025 · source -
Filter the vulnerabilities API to only return critical issues for a report.
GET /api/v1/vulnerabilities?severity=criticalRelease 20250925 · Sep 2025 · source
LDAP user synchronization shipped Automatically provisions users by synchronising accounts from Active Directory or OpenLDAP into the platform.
release 8 total
-
ldap_user_sync: Synchronize users from OpenLDAP or Microsoft Active Directory directories into Invicti Platform for automated provisioning. Release 20260709 (2026-07-09) · Jul 2026 · source · release history - New LDAP user synchronization: automates user provisioning from OpenLDAP or Microsoft Active Directory into Invicti Platform. Release 20260709 (2026-07-09) · Jul 2026 · source · release history
- LDAP user synchronization: Automate user provisioning by syncing from OpenLDAP or Microsoft Active Directory directly into Invicti Platform. Release 20260709 · Jul 2026 · source · release history
- SCIM integration with Microsoft Entra ID now uses long-lived OAuth tokens instead of short-lived bearer tokens Release 20260402 · Apr 2026 · source · release history
- Added SCIM user provisioning support for Invicti Ultimate users Release 20251106 · Nov 2025 · source · release history
- Reconstructed REST API specifications are now displayed in the API Discovery view Release 20251023 · Oct 2025 · source · release history
docs
-
Release 26.216.260804113742 Release date: 5 August 2026 LDAP user synchronization: You can now synchronize users from your LDAP directory (OpenLDAP or Microsoft Active Directory) into Invicti Platform, automating user provisioning and keeping team membership in sync with your directory.
docs update · Aug 2026
· source
example
-
Scan only API endpoints to reduce noise and improve speed compared to a full web app scan.
In the scan profile, enable 'API-only' capability for the target URL.Release 20251023 · Oct 2025 · source
API Catalog Integration Workflow shipped Enables direct creation of API targets from the API Catalog page with or without an attached specification and allows filtering displayed targets based on collection-level permissions.
release 7 total
-
Enables creating a new API target directly from the API Catalog page, with or without an API specification attached.
changelog · Sep 2026
· source
· release history
- Enables direct API target creation from the API Catalog page, with or without an attached API specification, without navigating to the Targets section first. Release 20260903 (2026-09-03) · Sep 2026 · source · release history
- API Catalog page now creates new targets with or without an attached specification without navigating to Targets Release 20260903 · Sep 2026 · source · release history
- API Catalog now filters displayed targets based on the user's collection-level permissions, removing the requirement to have account-wide target access. changelog · Aug 2026 · source · release history
- Adds permission-filtered view to the API Catalog, showing only targets accessible via collection-level permissions Release 20260820 · Aug 2026 · source · release history
- APIs discovered by a scan are linked back to that scan from the API catalog for traceability. Release 20260514 · May 2026 · source · release history
docs
- Release 20260903 Release date: 3 September 2026 API target creation from the API Catalog: You can now create a new API target directly from the API Catalog page, without navigating to the Targets section first. You can create the target with or without an API specification attached. docs update · Sep 2026 · source
Role Management Configuration shipped Makes all permission group operations visible and configurable in Role Management, giving administrators full control over custom role definitions.
Also counts toward: Role-based access control
release 7 total
-
Scopes API specification update permission to asset update permissions, allowing the ability to be granted without full API Security access.
Release 20261015 (2026-10-15) · Oct 2026
· source
· release history
-
Granular permission operations are now visible and configurable in Role Management, giving administrators full control over custom role definitions.
changelog · Sep 2026
· source
· release history
- Makes all permission group operations visible and configurable in Role Management, giving administrators full control over custom role definitions. Release 20260903 (2026-09-03) · Sep 2026 · source · release history
- Assigns the WAF upload permission group to Security Manager, Administrator, and Account Owner roles. Release 20260903 (2026-09-03) · Sep 2026 · source · release history
- Support access request capability added to Administrator role (no longer restricted to account owners). Release 20260528 (2026-05-28) · May 2026 · source · release history
- Allows administrators to request support access directly without requiring an account owner Release 20260528 · May 2026 · source · release history
AI-aided login recovery shipped suggested Uses AI to automatically recover a failed login sequence during a scan without operator intervention.
Suggested capability: Credentialed vulnerability scanning. This is our guess, not confirmed.
release
-
Extends
INVICTI_IGNORE_SSL_CHECKSenvironment variable to apply to all outbound platform API calls made during a scan (DAST, Inventory, Identity, and report/export endpoints)
Release 20260903 (2026-09-03) · Sep 2026
· source
· release history
- Adds AI-aided Login recovery: when an LSR playback fails during a scan, Invicti can now use AI to recover and complete authentication, reducing scan failures caused by login issues. changelog · Aug 2026 · source · release history
- New AI-aided Login setting enables AI recovery when Login Sequence Recorder (LSR) playback fails during a scan, reducing authentication-related scan failures. Release 20260625 (2026-06-25) · Jun 2026 · source · release history
- Invicti AI Assistant, including the Get help feature, is now available to all users in the account Release 20260514 (2026-05-14) · May 2026 · source · release history
- Invicti AI Assistant, including Get help, is now available to all users in the account. Release 20260514 · May 2026 · source · release history
docs
-
Release v26.9.1 Release date: 24 September 2026 Configurable authentication verifier timeout: Improved authentication verification by adding a configurable timeout setting, allowing you to prevent failures during slower login or single sign-on processes.
docs update · Sep 2026
· source
example
-
Enable AI-aided login recovery so scans can automatically recover from LSR playback failures without manual intervention.
In the Invicti console, open your scan policy or scan settings, locate the 'AI-aided Login' setting, and enable it.changelog · Aug 2026 · source
Automated vulnerability retesting shipped Allows users to configure automatic retesting of vulnerabilities after marking them as fixed and perform bulk retests on multiple findings simultaneously.
release
-
Adds Retest found vulnerabilities option in the Scan again dropdown on the scan summary to retest every vulnerability from a scan in one action.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Release 20261015 (2026-10-15) · Oct 2026
· source
· release history
- Added toggle in Settings to control automatic retest of vulnerabilities after selecting Fixed (Unconfirmed) status Release 20251106 · Nov 2025 · source · release history
example
-
Confirm all fixes from a completed scan in one step rather than retesting vulnerabilities individually.
On the scan summary page, open the `Scan again` dropdown and select `Retest found vulnerabilities` to queue a retest of every vulnerability the scan identified.
changelog · Oct 2026
· source
-
After deploying a fix, confirm all vulnerabilities from a scan are resolved without retesting each one individually.
In the scan summary, open the `Scan again` dropdown and select `Retest found vulnerabilities`.Release 20261015 (2026-10-15) · Oct 2026 · source -
Rerun a previous assessment with identical configuration to validate remediation quickly.
Click 'Repeat Scan' on the completed scan entry in the dashboard.Release 20260330 · Mar 2026 · source -
Retest multiple vulnerabilities at once from the dashboard or scan results.
In the UI, select multiple vulnerability entries and choose 'Bulk Retest'.Release 20251120 · Nov 2025 · source
Vulnerability browsing and filtering shipped Provides a vulnerabilities page where users can browse and filter findings by severity.
release
- Severity filter in the Vulnerabilities page expanded view is now available when browsing by individual vulnerability. Release 20260709 (2026-07-09) · Jul 2026 · source · release history
- Adds Collection filter on the Vulnerabilities page so you can narrow vulnerabilities down to specific collections alongside your other filters Release 20260611 · Jun 2026 · source · release history
- Persistent vulnerabilities view remembers grouped or ungrouped state across page loads Release 20260514 (2026-05-14) · May 2026 · source · release history
- Vulnerabilities page persists the last viewed grouped or ungrouped layout across sessions. Release 20260514 · May 2026 · source · release history
-
GET /api/v1/vulnerabilitiesaccepts a newseverityparameter to filter vulnerabilities by severity level Release 20250925 · Sep 2025 · source · release history - Added a filter on the Vulnerabilities page to show vulnerabilities found on APIs Release 20250828 · Aug 2025 · source · release history
Internal agent scan log retention shipped Lets administrators configure how long internal agents retain scan logs and where scan data is stored.
release
-
Configures how long internal agents retain scan logs and where they store scan data.
changelog · Oct 2026
· source
· release history
-
Configure internal agents to control how long they retain scan logs and where that data is stored
Release 20261001 (2026-10-01) · Oct 2026
· source
· release history
- Adds configurable internal agent scan log retention duration and storage path Release 20261001 · Oct 2026 · source · release history
- Adds configurable retention period and storage location for internal agent scan logs. Release 20261001 (2026-10-01) · Oct 2026 · source · release history
docs
- Release 20261001 Release date: 1 October 2026 Internal agent scan log retention: You can now configure how long internal agents keep scan logs and where they store scan data. docs update · Oct 2026 · source
Recon Agent for Non-Crawlable Surfaces shipped Allows the Recon agent to import architectural diagrams and documentation files (PDF, DOCX, MD) to discover attack surfaces that cannot be found through crawling.
release
-
The Recon agent can now import architectural diagrams and documentation files (PDF, DOCX, MD), enabling discovery of non-crawlable attack surfaces.
changelog · Sep 2026
· source
· release history
- Enables the Recon agent to import architectural diagrams and documentation files (PDF, DOCX, MD) to discover non-crawlable attack surfaces. Release 20260903 (2026-09-03) · Sep 2026 · source · release history
- Adds multimodal reference document imports: the Recon agent can now import architectural diagrams and documentation files (PDF, DOCX, MD) Release 20260903 (2026-09-03) · Sep 2026 · source · release history
-
Allows Recon agent to import
architectural diagramsand docs (PDF,DOCX,MD) as reference inputs. Agentic Pentesting: Release 20260831 · Aug 2026 · source · release history
example
-
Provide architectural context to the Recon agent to discover non-crawlable surfaces using uploaded documentation.
Upload `PDF`, `DOCX`, or `MD` files in the `Recon agent` settings under `Multimodal reference document imports`.Agentic Pentesting: Release 20260831 · Aug 2026 · source
Application dashboard enhancements shipped Adds visibility into application security posture through lists of most vulnerable technologies and engines with Rediscovered vulnerability counts.
release
-
Adds
asset namefilter on the Technologies page to narrow down identified technologies for a specific asset Release 20260611 (2026-06-11) · Jun 2026 · source · release history - The Executive and API Insights dashboards now include Rediscovered vulnerabilities in the total open counts Release 20251023 · Oct 2025 · source · release history
- Added an updates panel to the Application dashboard showing last scanned status and tags Release 20251023 · Oct 2025 · source · release history
- Application dashboard includes a new Most vulnerable technologies list Release 20250814 · Aug 2025 · source · release history
example
-
Filter technologies identified on a specific asset (e.g.,
app.invicti.com) on the Technologies pageIn the UI, go to Technologies > Filters > Asset Name and type 'app.invicti.com'Release 20260611 (2026-06-11) · Jun 2026 · source
Bulk actions for vulnerabilities shipped Provides bulk operations for vulnerability management, including export to file and synchronization.
release
- Enables Shift-select in lists (hold Shift and click another item) for bulk selection of Targets, Vulnerabilities, and Scans Release 20260611 · Jun 2026 · source · release history
- Adds a bulk action for retesting vulnerabilities. Release 20251120 · Nov 2025 · source · release history
- Added Export to file bulk action in Projects to export multiple items simultaneously Release 20250814 · Aug 2025 · source · release history
- Added Sync vulnerabilities bulk action in Projects for batch synchronization Release 20250814 · Aug 2025 · source · release history
example
-
Bulk-select a range of vulnerabilities by shift-clicking the first and last items in the list
In the UI, click the first vulnerability row, hold Shift, and click the last vulnerability row to select all in betweenRelease 20260611 (2026-06-11) · Jun 2026 · source
API specification export shipped Enables the export of discovered API specifications to external systems or downstream consumption workflows.
release
-
Adds API specification source location display in API Discovery, showing where each specification was found and which endpoints were auto-detected during a scan.
changelog · Sep 2026
· source
· release history
- Implemented API information export capability for API discovery and API catalog. Release 20251120 · Nov 2025 · source · release history
docs
- Release 20260917 Release date: 17 September 2026 API specification source location: In API Discovery, you can now see where each specification was found during the scan, making it easier to understand which endpoints were auto-detected and from which source. docs update · Sep 2026 · source
example
-
Export API specifications for downstream consumption without manual copy-paste.
Navigate to API Discovery or API Catalog and use the new export capability.Release 20251120 · Nov 2025 · source
Website Discovery and Filtering shipped Provides advanced filtering, risk score drilling, and programmatic export capabilities for discovered websites to streamline asset management and toolchain integration.
release
-
Clicking a count in the Website Discovery list now filters the list to show only entries matching that value.
changelog · Sep 2026
· source
· release history
- Improves Website Discovery filters with date range, exact match/exclusion text options, and multi-select risk score values Release 20260917 · Sep 2026 · source · release history
example
-
Retrieve discovered websites programmatically to feed into a cyber toolchain or SIEM.
GET /api/website-discoveryRelease 20260917 · Sep 2026 · source -
Drill into specific subsets of discovered websites by clicking the count badge for a risk score in the UI.
In Website Discovery, click the number next to a risk score value.Release 20260917 · Sep 2026 · source
Vulnerability Chaining Agent shipped An AI attack agent that correlates individual findings to execute multi-step vulnerability chains.
release
-
Adds a Vulnerability Chaining Agent that correlates individual findings to execute multi-step vulnerability chains, uncovering complex attack paths that single-step analysis might miss.
changelog · Sep 2026
· source
· release history
- Unveils the Vulnerability Chaining Agent: a new attack agent that correlates individual findings to execute multi-step vulnerability chains Release 20260903 (2026-09-03) · Sep 2026 · source · release history
- Adds a Vulnerability Chaining Agent to the Agentic Pentesting assessment engine, capable of correlating individual findings to execute multi-step attack chains. Release 20260903 (2026-09-03) · Sep 2026 · source · release history
- Introduces Vulnerability Chaining Agent to correlate findings into multi-step attack paths. Agentic Pentesting: Release 20260831 · Aug 2026 · source · release history
WebRTC Chatbot Detection shipped suggested Extends chatbot analysis capabilities to detect WebRTC data channels and SDP communications in real-time.
Suggested capability: Web vulnerability scanning. This is our guess, not confirmed.
release
-
Adds WebRTC data channel (SDP) chatbot detection, expanding chatbot coverage to applications using real-time communication protocols.
changelog · Sep 2026
· source
· release history
- Adds WebRTC data channel (SDP) chatbot detection, extending chatbot analysis to applications using real-time communication protocols. Release 20260903 (2026-09-03) · Sep 2026 · source · release history
- Detects and analyzes chatbots communicating via WebRTC data channels (SDP) in the target application Release 20260903 · Sep 2026 · source · release history
- Adds WebRTC chatbot detection capability: Invicti now detects and analyzes chatbots that communicate via WebRTC data channels (SDP) Release 20260903 (2026-09-03) · Sep 2026 · source · release history
Incremental scanning shipped suggested Enables targeted re-scanning of only changed assets or endpoints to quickly validate remediation without running a full assessment.
Suggested capability: Web vulnerability scanning. This is our guess, not confirmed.
Also counts toward: CI/CD pipeline integration
release
-
Adds
INVICTI_INCREMENTAL_SCANenvironment variable toscan-clifor limiting scans to new or changed endpoints Release 20260820 · Aug 2026 · source · release history
example
-
Run an incremental scan in CI/CD to target only changed endpoints and reduce execution time.
INVICTI_INCREMENTAL_SCAN=true ./scan-cli --target https://api.example.comRelease 20260820 · Aug 2026 · source -
Run incremental scans in CI/CD to only process new or changed endpoints, reducing scan time.
export INVICTI_INCREMENTAL_SCAN=true && ./scan-cli -t https://api.example.comRelease 20260820 (2026-08-20) · Aug 2026 · source -
Use incremental scans for immediate follow-up checks on changed code without re-scanning the whole app.
Initiate an 'Instant' scan and select 'Incremental mode' in the scan options.Release 20260330 · Mar 2026 · source
SCIM configuration auditing shipped Records who changed SCIM provisioning settings and when, providing an auditable history of access configuration changes.
Also counts toward: Administrative audit log
release
- Extends auditing to SCIM configuration changes, recording who changed provisioning settings and when in the audit log. Release 20260625 (2026-06-25) · Jun 2026 · source · release history
- Enables or disables SCIM2 provisioning endpoints per organization for Ultimate license customers Release 20260528 · May 2026 · source · release history
- Adds user provisioning with SCIM 2.0 for Teams Release 20250828 · Aug 2025 · source · release history
example
-
For Ultimate license admins wanting to prevent accidental user/team deletions via SCIM2, disable the provisioning endpoint for the organization.
Navigate to Organization Settings > Identity Management. Toggle 'SCIM2 Provisioning' off for this organization.Release 20260528 · May 2026 · source
Login Banner and Acknowledgment shipped Adds a configurable login warning banner with acknowledgment and decline options to support strict access control requirements.
release
- Adds a configurable login warning banner with acknowledgment and decline options for strict access control Release 20260416 (2026-04-16) · Apr 2026 · source · release history
- Adds a customizable header banner across all platform pages for organizational communications Release 20260416 (2026-04-16) · Apr 2026 · source · release history
- Adds a configurable login warning banner at login with acknowledgment and decline options for strict access control requirements Release 20260416 · Apr 2026 · source · release history
example
-
Display a critical security notice to all users immediately upon accessing any platform page.
Set up a customizable banner in the platform's header configuration settingsRelease 20260416 · Apr 2026 · source
Trend Matrix shipped Provides a visual view of Mean Time to Remediate (MTTR) grouped by severity for targets or applications, including CSV export capabilities.
Also counts toward: CSV data export
release
- The Application Trend Matrix UI gains a 'view by time range' dropdown for trend analysis Release 20250925 · Sep 2025 · source · release history
- Introduces the Trend Matrix for Applications as a new view displaying Mean Time to Remediate grouped by severity and indicating vulnerabilities exceeding MTTR Release 20250911 · Sep 2025 · source · release history
- Adds the ability to export the Trend Matrix to CSV format Release 20250911 · Sep 2025 · source · release history
- Implements Trend Matrix for DAST Targets Release 20250828 · Aug 2025 · source · release history
CI/CD Source Scan API Key Authentication shipped Enables reliable long-lived API key authentication for Source Scans in CI/CD pipelines, with configurable expiry dates to replace short-lived tokens.
Also counts toward: CI/CD pipeline integration
release
-
Adds API key authentication for Source Scan in CI/CD pipelines, with expiry date support on the Profile API key page, so pipelines no longer depend on short-lived tokens.
Release 20261015 (2026-10-15) · Oct 2026
· source
· release history
example
-
Authenticate a CI/CD Source Scan with a long-lived API key instead of a short-lived token so repeated pipeline jobs stay reliable.
In Invicti Platform, go to Profile > API key, generate an API key with an expiry date, then supply it as the authentication credential in your Source Scan CI/CD pipeline configuration.
changelog · Oct 2026
· source
-
Authenticate a long-running pipeline Source Scan with an API key rather than a short-lived token, and set an expiry date for the key.
Navigate to `Profile API key`, generate an API key for Source Scan, set the desired expiry date, and configure your CI/CD pipeline to pass the key as the authentication credential.Release 20261015 (2026-10-15) · Oct 2026 · source
Target CSV export shipped Exports the full list of scan targets to CSV, including tags, vulnerability counts, and last scan date.
Also counts toward: CSV data export
release
-
Adds agents column to the CSV sitemap export, listing which agents tested each endpoint.
changelog · Oct 2026
· source
· release history
-
Adds agent columns to the CSV sitemap export, listing which agents tested each endpoint.
Release 20261001 (2026-10-01) · Oct 2026
· source
· release history
- CSV exports of targets now include tags, vulnerability counts, and last scan date for richer bulk reporting. Release 20260625 (2026-06-25) · Jun 2026 · source · release history
On-premises Linux installation shipped suggested Installs Invicti Platform on-premises on Linux using support-provided scripts for RHEL-compatible distributions, Ubuntu, and Debian.
Suggested capability: Web vulnerability scanning. This is our guess, not confirmed.
Also counts toward: Self-hosted deployment
release
-
The scalable internal scanning agent Helm chart now supports deployment on OpenShift and Red Hat OpenShift Service on AWS (ROSA) clusters.
changelog · Sep 2026
· source
· release history
docs
- Install on Linux Install Invicti Platform on-premises on Linux using support-provided installation scripts for RHEL-compatible distributions, Ubuntu, and Debian. seen Oct 2026 · source
-
Release 26.243.260831140137 Helm chart: 26.243.260831140137 Windows installer: 26.9.2.1328 Release date: 1 September 2026 Custom Security Checks: You can now create and run custom security checks in your on-premises deployment, extending DAST scan coverage with checks designed for your specific environment and…
docs update · Sep 2026
· source
Vulnerability-to-issue tracker automation shipped Automatically pushes vulnerability details to external issue trackers, creating or updating work items upon discovery.
Also counts toward: Ticketing integration
release
-
Adds
{Asset URL}placeholder support in Jira, Azure Boards, GitHub, and GitLab integration field mappings.
changelog · Aug 2026
· source
· release history
- Adds custom Jira fields of type Label to integration field mapping, enabling automatic tagging of Jira issues created by Invicti. changelog · Aug 2026 · source · release history
- Automation now pushes vulnerabilities to issue trackers upon discovery, creating or updating work items automatically Release 20250814 · Aug 2025 · source · release history
Collections dashboard shipped Shows a dashboard summarising the security posture of a collection of targets at a glance.
release
- Adds a dedicated dashboard for Collections, providing at-a-glance security posture visibility at the collection level. Release 20260625 (2026-06-25) · Jun 2026 · source · release history
- Improves asset visibility in collections so mapped application assets appear automatically without manual mapping Release 20260416 (2026-04-16) · Apr 2026 · source · release history
example
-
Monitor the security posture of a specific collection without navigating to individual applications.
Collections > [Select Collection] > DashboardRelease 20260625 (2026-06-25) · Jun 2026 · source
Org-wide scan suspension shipped Lets administrators pause all scheduled scans across the organisation in one action.
release
- Adds organization-level ability to suspend all future scheduled scans across the account Release 20260625 (2026-06-25) · Jun 2026 · source · release history
- New Suspend all scheduled scans control lets organization administrators pause all future scheduled scans across the account in one action. Release 20260625 (2026-06-25) · Jun 2026 · source · release history
example
-
Pause all automated scanning org-wide during a change-freeze window without touching each schedule individually.
In the Invicti console, go to Scheduled Scans and use the Suspend All Scheduled Scans control to halt every future scheduled scan across the account at once.Release 20260625 (2026-06-25) · Jun 2026 · source
Vulnerability database tagging shipped Tags detected vulnerabilities with labels such as 'API' to distinguish them from standard web vulnerabilities.
release
-
Expands tag support to accept any character, including spaces and multiple
:separators, across all services Release 20260416 (2026-04-16) · Apr 2026 · source · release history - Enables adding bulk comments and tags to vulnerabilities Release 20251204 · Dec 2025 · source · release history
-
API targets are now tagged with an
APIlabel on detected vulnerabilities to distinguish them from web vulns Release 20250925 · Sep 2025 · source · release history
Vulnerability severity management shipped suggested Allows users to manually adjust the severity of discovered vulnerabilities to match internal risk models or triage workflows.
Suggested capability: Vulnerability prioritization. This is our guess, not confirmed.
release
-
overridesnow allow users to manually override the severity of vulnerabilities detected in DAST scans. Release 20260205 (2026-02-05) · Feb 2026 · source · release history - Adds the ability to override the severity of vulnerabilities detected in DAST scans for individual findings or globally Release 20260205 · Feb 2026 · source · release history
example
-
Manually adjust a detected vulnerability's severity to better match your internal risk tolerance.
In the vulnerability details view, locate the 'Severity' field and select 'Override'.Release 20260205 (2026-02-05) · Feb 2026 · source
API operation details in catalog shipped Enhances the API catalog to display detailed information about individual API operations and reconstructed specifications.
Also counts toward: REST API
release
- Adds preview capability for REST API specifications (OpenAPI, Swagger, RAML) after upload Release 20251204 · Dec 2025 · source · release history
- Adds URL reference support in target settings to load API specs at runtime from targets not accessible to Invicti cloud services Release 20251204 · Dec 2025 · source · release history
example
-
View newly discovered APIs and their reconstructed specifications directly from the discovery interface.
Navigate to the API Discovery view to see reconstructed REST API specifications and filtered third-party APIs.Release 20251023 · Oct 2025 · source
API catalog notifications and filtering shipped Notifies users via bell alerts and email when APIs are discovered or updated, and provides a 'Requires scanning' filter in the API catalog to surface endpoints that have not yet been DAST scanned.
release
-
Receive bell notifications and emails when APIs are discovered or updated, with a direct link to the changed APIs in the API catalog; turn off email alerts in your profile notification settings.
Release 20261028 (2026-10-28) · Oct 2026
· source
· release history
- Filter the API catalog by newly discovered or recently updated APIs using the new Requires scanning filter to find endpoints that still need a DAST scan. Release 20261028 (2026-10-28) · Oct 2026 · source · release history
API Exclusion Management shipped Replaces 'Hide API' with an 'Exclude API' action that labels APIs as third-party and requires a reason for exclusion in API Discovery.
release
-
Adds an Exclude API action in API Discovery (replacing Hide API) that labels APIs as third-party and requires a reason for exclusion.
changelog · Aug 2026
· source
· release history
example
-
Exclude a detected third-party API from discovery results so it no longer appears in the API Catalog.
In API Discovery, locate the API, open its action menu, select 'Exclude API', choose 'Third-party' as the type, and enter a reason for the exclusion.changelog · Aug 2026 · source
SSO Registration Settings shipped Displays an organization-specific SSO identifier on the SSO settings page to simplify SAML registration and configuration.
release
- Adds Organization-specific SSO identifier displayed in the SSO settings page for SAML registration Release 20260820 · Aug 2026 · source · release history
- Displays an organization-specific SSO identifier on the SSO settings page for SAML registration Release 20260820 (2026-08-20) · Aug 2026 · source · release history
Vulnerability state persistence shipped suggested Carries forward triage decisions such as Ignored or False Positive so they are not lost when a new scan runs.
Suggested capability: Web vulnerability scanning. This is our guess, not confirmed.
release
- Vulnerability states (Ignored, False Positive) are now persisted and carried forward into subsequent DAST scans. Release 20260709 (2026-07-09) · Jul 2026 · source · release history
- Persistent vulnerability state carries Ignored and False Positive states from previous DAST scans into subsequent runs without resetting. Release 20260709 · Jul 2026 · source · release history
Target Configuration Change Auditing shipped Captures previous and new values for critical target configuration changes such as business criticality, authentication settings, and scan configurations in audit logs.
release
- Improved auditing captures previous and new values for Target configuration changes (business criticality, authentication, etc.). Release 20260514 · May 2026 · source · release history
- Auditing for Target configuration changes now captures previous and new values for business criticality, authentication, scan configuration, agent settings, excluded hours, IAST settings, name, and tags Release 20260514 (2026-05-14) · May 2026 · source · release history
Workspace isolation shipped Provides isolated, self-managed environments for different teams, projects, or scopes within an organization to manage scans and assets independently.
release
- Adds Workspaces to create isolated, self-managed environments for teams, projects, or scopes within an organization. Release 20260514 · May 2026 · source · release history
- Adds Workspaces to create isolated, self-managed environments for teams, projects, or independent organization Release 20260514 (2026-05-14) · May 2026 · source · release history
API Discovery from Source Code shipped suggested Adds the ability to discover APIs by analyzing source code using Invicti Source Scan, expanding the API inventory beyond live traffic.
Suggested capability: Static application security testing. This is our guess, not confirmed.
release
- Adds API Discovery from source code using Invicti Source Scan to expand your API inventory without relying solely on live traffic Release 20260416 · Apr 2026 · source · release history
- Adds Invicti Source Scan to discover APIs directly from source code, expanding inventory without live traffic dependency Release 20260416 (2026-04-16) · Apr 2026 · source · release history
Automated scan report delivery shipped Allows configuration of automated email notifications containing scan reports upon scan completion.
release
- Implemented a new automation feature to automatically email a specified scan report upon scan completion Release 20251023 · Oct 2025 · source · release history
example
-
Automate report delivery by configuring the system to email a specific recipient upon completion.
Configure the new automation feature in Settings > Automation to trigger an email with the scan report.Release 20251023 · Oct 2025 · source
CSV import with authentication shipped suggested Supports importing targets via CSV files, including the specification of username and password for form-based authentication.
Suggested capability: Credentialed vulnerability scanning. This is our guess, not confirmed.
release
- CSV import of Targets allows specifying username and password for form authentication Release 20251009 · Oct 2025 · source · release history
example
-
Import targets with form auth credentials via CSV
Include 'username' and 'password' columns in your target CSV file before importing into InvictiRelease 20251009 · Oct 2025 · source
Scan duration configuration shipped Allows administrators to set maximum scan durations per target or for CI/CD pipeline targets.
release
- DeepScan now scans all path fragments discovered in locations for potential vulnerabilities Release 20250828 · Aug 2025 · source · release history
example
-
Set a short scan duration (e.g. 30 seconds) for a fast CI/CD pipeline target.
POST /api/v1/targets/<id>/settings { "max_scan_duration": 30 }Release 20250925 · Sep 2025 · source
Scan scheduling from target context shipped Allows users to initiate new scans or schedule them directly from a specific target's view without navigation.
release
-
The
/targets/<id>/drawerin the UI now allows creating a new scan schedule directly from the target view Release 20250925 · Sep 2025 · source · release history
example
-
Schedule a new scan for a specific target without leaving the target's context.
In the Invicti UI, open the Target drawer and select 'Create Scan Schedule'.Release 20250925 · Sep 2025 · source
Sensitive data classification in API catalog shipped Labels each API and endpoint in the catalog with the category of sensitive data it exposes — Secrets, PII, or Financials — making risk visible at a glance without opening individual findings.
release
-
API catalog and API discovery now label each API and endpoint with the category of sensitive data it exposes — Secrets, PII, or Financials — so risk is visible without opening each finding.
Release 20261028 (2026-10-28) · Oct 2026
· source
· release history
SCIM User Lifecycle Management shipped Extends SCIM provisioning capabilities to include bulk user removal operations for efficient identity lifecycle management.
release
-
Adds bulk removal of SCIM-provisioned users from Invicti Platform in a single operation.
Release 20261015 (2026-10-15) · Oct 2026
· source
· release history
Saved filter sharing documented Allows users to share saved filters with other members of their organization so teams can work from consistent views without recreating them.
docs
- Release 20261008 Release date: 8 October 2026 Shared saved filters: You can now share your saved filters with other users in your organization, so teams can work from the same views without recreating them. docs update · Oct 2026 · source
Authentication Verifier Timeout Configuration documented Adds a configurable timeout setting for authentication verification to prevent failures during slower login or single sign-on processes.
docs
-
Release v26.9.1 Release date: 24 September 2026 Configurable authentication verifier timeout: Improved authentication verification by adding a configurable timeout setting, allowing you to prevent failures during slower login or single sign-on processes.
docs update · Sep 2026
· source
Dedicated authentication header configuration shipped suggested Allows targets to be configured with dedicated authentication headers separate from functional headers for more precise access control.
Suggested capability: Credentialed vulnerability scanning. This is our guess, not confirmed.
example
-
Configure a target to use dedicated authentication headers instead of functional headers
In the target configuration, set `Bearer Token` or `API Key` as the authentication type.
Release 20260903 · Sep 2026
· source
Scan Confidence Threshold Configuration shipped suggested Adds a configurable minimum confidence threshold setting that causes a scan to fail if the threshold is exceeded, independent of severity settings.
Suggested capability: Web vulnerability scanning. This is our guess, not confirmed.
release
-
Adds
INVICTI_MINIMUM_CONFIDENCEenvironment variable: setting it independently causes a scan to fail when the threshold is exceeded (no longer requiringINVICTI_MINIMUM_SEVERITY)
Release 20260903 (2026-09-03) · Sep 2026
· source
· release history
Machine-readable scan result export shipped Exports scan results in structured, machine-readable formats tailored for CI/CD pipelines and external security analysis tools.
Also counts toward: CI/CD pipeline integration
example
-
Export scan results in machine-readable formats for CI/CD integration or external analysis pipelines.
Click `Download Report` and select `JSON` or `Markdown (.md)` from the export options.Agentic Pentesting: Release 20260831 · Aug 2026 · source
Large Payload Download Support shipped suggested Offers request and response payloads over 2 MB in vulnerability details as downloads instead of inline rendering to support very large scan results.
Suggested capability: Web vulnerability scanning. This is our guess, not confirmed.
release
-
Request and response payloads over 2 MB in vulnerability details are now offered as a download instead of being rendered inline, supporting very large scan results.
changelog · Aug 2026
· source
· release history
SSO Certificate Format Support shipped Supports SSO login for organizations using identity provider certificates stored in bare base-64 DER format.
release
-
Adds SSO login support for organizations whose identity provider certificate is stored in bare base-64 DER format.
changelog · Aug 2026
· source
· release history
Ordinal monthly scan scheduling shipped Schedules scans to run on a specific weekday of a chosen month, such as the first Monday.
Also counts toward: Scheduled jobs
release
- Adds ordinal monthly scan scheduling, allowing scans to be scheduled on a specific weekday of the month (e.g., first Monday, second Thursday). Release 20260625 (2026-06-25) · Jun 2026 · source · release history
Auto-scalable scan infrastructure shipped Provisions agent resources dynamically to scale scan infrastructure based on workload demands.
Also counts toward: Agent-based deployment
release
- Introduces Auto-scalable agents for scan infrastructure Release 20251204 · Dec 2025 · source · release history
WAF detection reporting shipped Identifies and reports Web Application Firewalls detected by the DAST scanner within the scan activity log.
release
- Reports WAFs detected by DAST scanner in the Scan activity log Release 20251204 · Dec 2025 · source · release history
Hostname variation handling shipped suggested Improves crawling scope accuracy by treating different subdomain formats of the same hostname as within the same scope.
Suggested capability: Web vulnerability scanning. This is our guess, not confirmed.
release
- Implemented hostname variation handling during web crawling to ensure links with different subdomain formats are considered within the same scope. Release 20251120 · Nov 2025 · source · release history
User list filtering shipped Allows administrators to filter the user management view by provisioning method to distinguish between manually created and auto-provisioned accounts.
release
- Added ability to filter the user list by user creation method (manually created vs. auto-provisioned) Release 20251106 · Nov 2025 · source · release history
Internal Agent resource specifications shipped Defines required hardware specifications (CPU, RAM, disk) for Internal Agents to ensure stable performance.
release
- Updated requirements for the Internal Agent to specify CPU, RAM, and disk space Release 20251023 · Oct 2025 · source · release history
CI/CD Scan Profile requirements shipped Enforces the use of explicit scan profiles for CI/CD integrations, migrating prior configurations if necessary.
release
- Scan Profiles are now required for CI/CD integrations; prior configurations without explicit profiles may fail or require migration. Release 20250911 · Sep 2025 · source · release history
Scan comparison shipped Enables users to view and compare results from past scans to identify changes in vulnerability states or counts.
release
- Past scans tab includes a new Scan comparison feature Release 20250814 · Aug 2025 · source · release history
Vulnerability assignment shipped Allows users to assign discovered vulnerabilities to specific team members for triage and remediation tracking.
release
- Vulnerabilities can be assigned to a specific user via the assignment interface Release 20250814 · Aug 2025 · source · release history
Vulnerability consolidation reporting shipped suggested Generates standard and compliance reports that aggregate vulnerabilities across all SAST assets within an application for a unified overview.
Suggested capability: Static application security testing. This is our guess, not confirmed.
release
- Standard and compliance reports can now consolidate all SAST asset vulnerabilities for an application overview Release 20250814 · Aug 2025 · source · release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
4 commands for Invicti, each with where it came from. This tool has no source analysis yet, so there is no option reference and no captured run beside them.
No command matches.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for Invicti, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Invicti puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Commercials
pricing & packaging history · Invicti (Netsparker) vendor page40 readings of Invicti (Netsparker)'s pricing page since Mar 2022, with 5 relaunches of its plan lineup and 8 changes to what its plans include — each one dated, compared with the reading before it, and explained for someone buying the tool.
Pricing and packaging history is included with Researcher and Business. See how every vendor we track sells, and how that has changed over time, using data we don't publish anywhere else.
See plans → Already subscribed? Sign in →Plans by offering
Each offering on the pricing page links to its own page of plans, read at its latest capture.
Plan relaunches
Plans, prices and descriptions are quoted from the vendor's own pricing page as we read it on each date. A plan missing from a later reading is shown as no longer listed on the page — a statement about the page, not the product. Readings that failed to show any plans are left out rather than read as a change.
Website history
invicti.com, every changeInvicti (Netsparker)'s home and pricing pages and 38 more pages as they looked each month from September 2021 to October 2026: 64 renders, 10 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Coverage
Missing something? Tell us
What Invicti connects to, runs on and detects, read from its release notes and docs. So far: 2 new detections, 1 new supported platform.
3 changes, tracked since Oct 2, 2026.
-
Oct 52026
new Ruby deserialization, JWT authentication bypass, and path traversal blocklist bypass detection
With Ruby deserialization vulnerabilities, JWT authentication bypass techniques, path traversal that bypasses simple blocklist filters
Attack agents now detect more vulnerability variants, including Ruby deserialization vulnerabilities, additional JWT authentication bypass techniques, and path traversal that bypasses simple blocklist filters. The credential brute-force agent also now identifies login fields more accurately.
-
Oct 52026
new Install on Linux
-
Oct 22026
new Ruby deserialization vulnerability detection
With Ruby deserialization vulnerabilities, JWT authentication bypass techniques, path traversal that bypasses simple blocklist filters
Attack agents now detect more vulnerability variants, including Ruby deserialization vulnerabilities, additional JWT authentication bypass techniques, and path traversal that bypasses simple blocklist filters.
Operating systems 1
Nothing first seen in this window. That doesn't mean Invicti shipped nothing, only that we found no record of it.
How we count
Read from 8 of 78 release notes and docs updates we hold for Invicti. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through Invicti's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
78 entries
No entries match these filters.
- October 202611
- September 202614
- August 202610
- July 20268
- June 20264
- May 20264
- April 20266
- March 20264
- February 20264
- January 20263
- December 20251
- November 20252
- October 20252
- September 20252
- August 20252
- July 20251
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →