MISP
v2.5.50 open-sourceThe section your link pointed to isn't on MISP's page any more, so we've brought you to the top.
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
curl -s -H 'Authorization: <api-key>' -H 'Accept: application/vnd.openxmlformats-officedocument.spreadsheetml.sheet' 'https://<misp-host>/attributes/restSearch/returnFormat:xlsx/type:ip-dst' -o results.xlsx
curl -s -H 'Authorization: <api-key>' -H 'Accept: application/vnd.openxmlformats-officedocument.spreadsheetml.sheet' 'https://<misp-host>/attributes/restSearch/returnFormat:xlsx/escape_formulas_literal:1' -o results_literal.xlsx
cake Admin migrationStatus
cake Admin migrationApply --dry-run
curl https://<misp-instance>/gpg.asc
# In app/Config/config.php or equivalent OIDC config block:
'OidcAuth' => [
    'button_text' => 'Login with CorpSSO',
    ...
]
curl -s -H 'Authorization: <your-api-key>' -H 'Accept: application/json' -H 'Content-Type: application/json' -X POST https://<misp-instance>/servers/updateJSON -d '{"background": true}'
app/Console/cake Admin migrateOldTemplates
app/Console/cake Admin setSetting Plugin.Geolocation_enabled true
app/Console/cake Admin setSetting Plugin.Geolocation_url "https://tiles.example.com"
app/Console/cake CLI 1
/var/www/MISP/app/Console/cake Admin setSetting "MISP.enable_themes" 1
docker exec -it misp-docker-misp-core-1 /var/www/MISP/app/Console/cake Admin setSetting "MISP.enable_themes" 1
curl -s -H 'Authorization: <your-api-key>' -H 'Accept: application/json' -H 'Content-Type: application/json' -X POST https://<misp-host>/galaxies/exportGalaxyClusters -d '{"default": true, "custom": true, "distribution": [0, 1, 2]}'
/var/www/MISP/app/Console/cake Admin preRelease
curl -X POST https://<misp-instance>/events/recorrelate/<event_id> -H 'Authorization: <api_key>' -H 'Accept: application/json'
cake Admin runDBScript highPerformance
GET /diagnostic/slowSql
cake Admin runDBScript highPerformance
cake Admin runDBScript indexLogs
curl -H 'Authorization: <api_key>' -H 'Accept: application/json' 'https://<misp>/attributes/restSearch' -d '{"object_relation": "ip-dst"}'
curl -s -X POST -H 'Authorization: <your-api-key>' -H 'Content-Type: application/json' -H 'Accept: application/json' -d '{"value": "<ioc-value>", "warninglist": 1}' 'https://<misp-instance>/attributes/search'
GET /collections/view/<uuid>
curl -H 'Authorization: <your-api-key>' -H 'Accept: application/json' 'https://<misp-instance>/events/restSearch/returnFormat:kunai'
curl -H 'Authorization: <your-api-key>' -H 'Accept: application/json' -H 'Content-Type: application/json' -X POST https://<misp-instance>/events/restSearch -d '{"returnFormat": "kunai", "tags": ["<tag>"]}'
bash INSTALL/INSTALL.ubuntu2404.sh
bash INSTALL/UPGRADE.ubuntu2404.sh
curl -s -D - -H 'Authorization: <api_key>' -H 'Accept: application/json' -H 'Content-Type: application/json' -X POST https://<misp_instance>/attributes/restSearch -d '{"returnFormat":"json","sort":"publish_timestamp","page":2,"limit":100}' | grep -E '(X-Skipped-Elements-Count|^{)'
{
  "selector_type": "event_info",
  "selector_list": [
    "%] Daily scan results",
    "Weekly scan results week #%"
  ]
}
curl -s -o /dev/null -w '%{http_code}' https://<misp_host>/users/heartbeat
curl -H 'Authorization: <api_key>' https://<misp_host>/users/view/<user_id>.json | jq '.User.totp'
curl -X POST https://misp.local/attributes/enrich/[attribute_id] \
  -H 'Authorization: YOUR_AUTH_KEY' \
  -d '{"dns": 1}'
curl -H 'X-MISP-AUTH: <your_api_key>' https://misp.example.com/attributes/restSearch
curl -X GET "https://misp.example.org/events/restSearch?includeGranularCorrelations=1" -H "Authorization: <key>"
curl -X GET "https://misp.example.org/events/restSearch?orgc_id=12345" -H "Authorization: <key>"
curl -X POST 'https://<misp_host>/tags/modifyTagRelationship/attribute/<attribute_id>' -H 'Authorization: <key>' -H 'Accept: application/json'
[workflow]
scoping = ["local", "relationship"]
# ... other settings
GET /api/events/restSearch?event_tags='exploit,cve-2023'
GET /api/events/restSearch?static=1&include_proposals=false
curl -s 'https://misp-server/api/events/restSearch?sharing_group=123&authkey=YOUR_KEY' | jq '.Event[0].id'
{
   "AND": {
       "OR": {
           "org_sector": "Financial",
           "sharing_group_id": 127
       },
       "NOT": {
           "org_nationality": [
               "Russia",
               "Russian Federation",
               "Belarus",
               "Republic of Belarus"
           ]
       }
   }
}
curl -k -H 'Authorization: <YOUR_API_KEY>' -H 'Accept: application/json' 'https://<MISP_HOST>/attributes/restSearch?returntype=stix2&search=<your_search_criteria>'
python /var/www/MISP/app/Lib/cake.php Console/Test alert_email_template
bin/cake MISP.ServerList
python /opt/misp/PyMISP/scripts/generate_community_page.py
MISP/app/Console/cake Admin UserIP <user_id>
MISP/app/Console/cake Admin IPUser <ip>
GET /attributes/restSearch?timestamp=3600&attribute_timestamp=true
curl -X POST 'https://<misp>/attributes/restsearch' \
  -H 'Authorization: <auth>' \
  -H 'Content-Type: application/json' \
  -d '{
    "galaxy.cfr-suspected-victims": ["China", "Japan"]
  }'
/var/www/MISP/app/Console/cake resetSyncAuthkeys
curl -X GET "https://misp.local/attributes/restSearch" \
  -H 'Authorization: YOUR_API_KEY' \
  -H 'Content-Type: application/json' \
  -d '{
    "search": {"category": "Network activity"},
    "includeSightings": true,
    "includeCorrelations": true
  }'
# Create the event ID first if needed, then add attribute
# Using PyMISP or API with new type
curl -X POST "https://misp.local/events/addAttribute/12345" \
  -H 'Authorization: YOUR_API_KEY' \
  -d '{
    "attribute": {"value": "CWE-79", "type": "weakness (CWS)"}
  }'
# Via MISP API or UI when adding attributes
{ "type": "cdhash", "value": "<code_signing_hash>" }
{ "type": "ja3-fingerprint-md5", "value": "<ssl_fingerprint>" }
curl -s -H 'Authorization: <token>' 'https://<misp-host>/events/restSearch/attribute/value:<value>?includeProposals=1'
curl -k -H 'Authorization: YOUR_KEY' -H 'Accept: application/json' 'https://misp.example.com/restSearch/event?limit=100&page=2'
POST /objects/add with body containing "template_uuid": "<uuid>", "version": <version_number>
/var/www/MISP/app/Console/cake Admin getSetting
/var/www/MISP/app/Console/cake Admin setSetting "Plugin.Import_services_enable" 1
In the Users menu, click the 'Export My Data' button to download your MISP information.
curl -X POST 'https://<misp>/sharingGroups/addOrg/<sg_id>/<org_id>/0' -H 'Authorization: <auth_key>'
GET https://<misp-instance>/events/csv/download/<event-id>?attributes=timestamp,type,uuid,value
GET https://<misp-instance>/events/csv/download/<event-id>?attributes=timestamp,type,uuid,value&object_attributes=uuid,name
Summary
MISP is an open-source threat intelligence platform for collecting, storing, and sharing cyber security indicators and malware information, and it costs nothing to use. It runs as a self-hosted web application, typically deployed on an organisation's own server, with an admin CLI for managing events, attributes, and users from the terminal alongside the web interface. It is built for incident analysts, security and ICT professionals, and malware reversers who need to exchange structured threat data with peers and feed it into NIDS, log analysis tools, and SIEMsSIEMsSecurity Information and Event Management platforms that collect, normalize, and correlate log data across an infrastructure so cyber tools can detect threats and trigger alerts from a central point.. It supports standard sharing protocols like TAXIITAXIIA protocol for sharing threat intelligence over HTTPS, commonly carrying STIX data. It lets tools retrieve and exchange intelligence from compatible services. for pushing indicators to other servers, and it ships with default feeds from providers such as PrecisionSec and SiberKapan, positioning it within the broader IOCIOCAn indicator of compromise, an observable clue that may point to malicious activity, such as a suspicious file hash or domain. It is evidence to investigate, rather than proof by itself.-sharing and feed-consumption space rather than as a standalone analysis tool. Development is active, with over 2,000 commits in the past year and a release only 39 days ago.
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
How MISP helps
Which indicators from my past incidents overlap with what a new event is reporting?
correlation-based matching surfaces events sharing indicators with your organisation's data, so a new report can be checked against everything already collected before deciding it is novel
Which threat actors and techniques are trending across the events stored here?
dashboard widgets aggregate stored events into trending vulnerability, threat-actor, and ATT&CK technique views, with a heatmap showing which techniques and sub-techniques actually appear in your data versus ones never seen
Where did a given indicator or event come from, and can I push it onward automatically?
events and attributes carry their source and sharing-group metadata, and a scheduled task can push matching events out over TAXII on a timer or on demand, so outbound sharing does not depend on someone remembering to do it
Can I tag and classify a batch of events without opening each one?
mass tagging and galaxy cluster attachment apply from the event index to multiple selected events at once, rather than one at a time
Which of my events should never leave this system once flagged?
a workflow action can write matched attributes to a blocklist file, grouped by tag and removable by tag, so a designation made once is enforced automatically on later matches
Do these indicators correspond to a real place, and does that change how I read them?
objects carrying geographic coordinates render on a map with accuracy-radius circles, GeoJSON shapes, and GPX tracks, so location-tagged indicators can be inspected visually rather than as raw coordinates
Languages
Features
Built from MISP's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- MISP covers 5 of the 8 investigation and response capabilities we track.
What MISP offers you
- REST API20
- Command-line interface7
- Scheduled jobs3
- CSV data export2
- JSON data export2
- Role-based access control2
- Administrative audit log1
- Plugin system1
- SIEM forwarding1
- STIX and TAXII1
- Web management console1
No capabilities match.
Threat indicator matching 4 features Investigation and response since 2020
Warning list additions shipped Adds specific warning lists for captive portals, parking pages, and cached Chrome top websites to improve threat detection accuracy.
Shared capability: Threat indicator matching
release
- Adds Cisco umbrella block pages and Censys scanning IP address space to warning-lists. v2.4.176 · Sep 2023 · source · release history
-
Adds
captive-portalswarning list to detect captive portal networks v2.4.169 · Mar 2023 · source · release history - Adds new warning-list generators for Cached Chrome Top Million Websites and improved gzip file source support v2.4.168 · Feb 2023 · source · release history
Warninglist Script Generator shipped Fetches Windows binary hashes and generates corresponding warninglists automatically.
Shared capability: Threat indicator matching
release
- New misp-warninglists script to fetch Windows binary hashes and generate a warninglist from them. v2.5.37 · Apr 2026 · source · release history
Advanced attribute correlation shipped Expands correlation capabilities to include new attribute types like CIDR ranges and PGP keys, and supports dynamic decay modeling based on sighting true/false positives.
Shared capability: Threat indicator matching
release
- New DecayingModel leverages true positive and false positive sightings for improved attribute scoring decisions. v2.4.196 · Aug 2024 · source · release history
Attribute type correlation extensions shipped Adds logic to correlate specific new attribute types such as CIDR ranges for IPs and PGP keys.
Shared capability: Threat indicator matching
release
-
Enables CIDR-based correlation logic for
ip-src|portandip-dst|portattribute types v2.4.128 · Jun 2020 · source · release history
Response playbook automation 1 feature Investigation and response since 2024
Ad-hoc workflow execution shipped Provides the ability to run workflows independently of application triggers, allowing manual or scheduled execution against specific events.
Shared capability: Response playbook automation
Also counts toward: Scheduled jobs
release 7 total
-
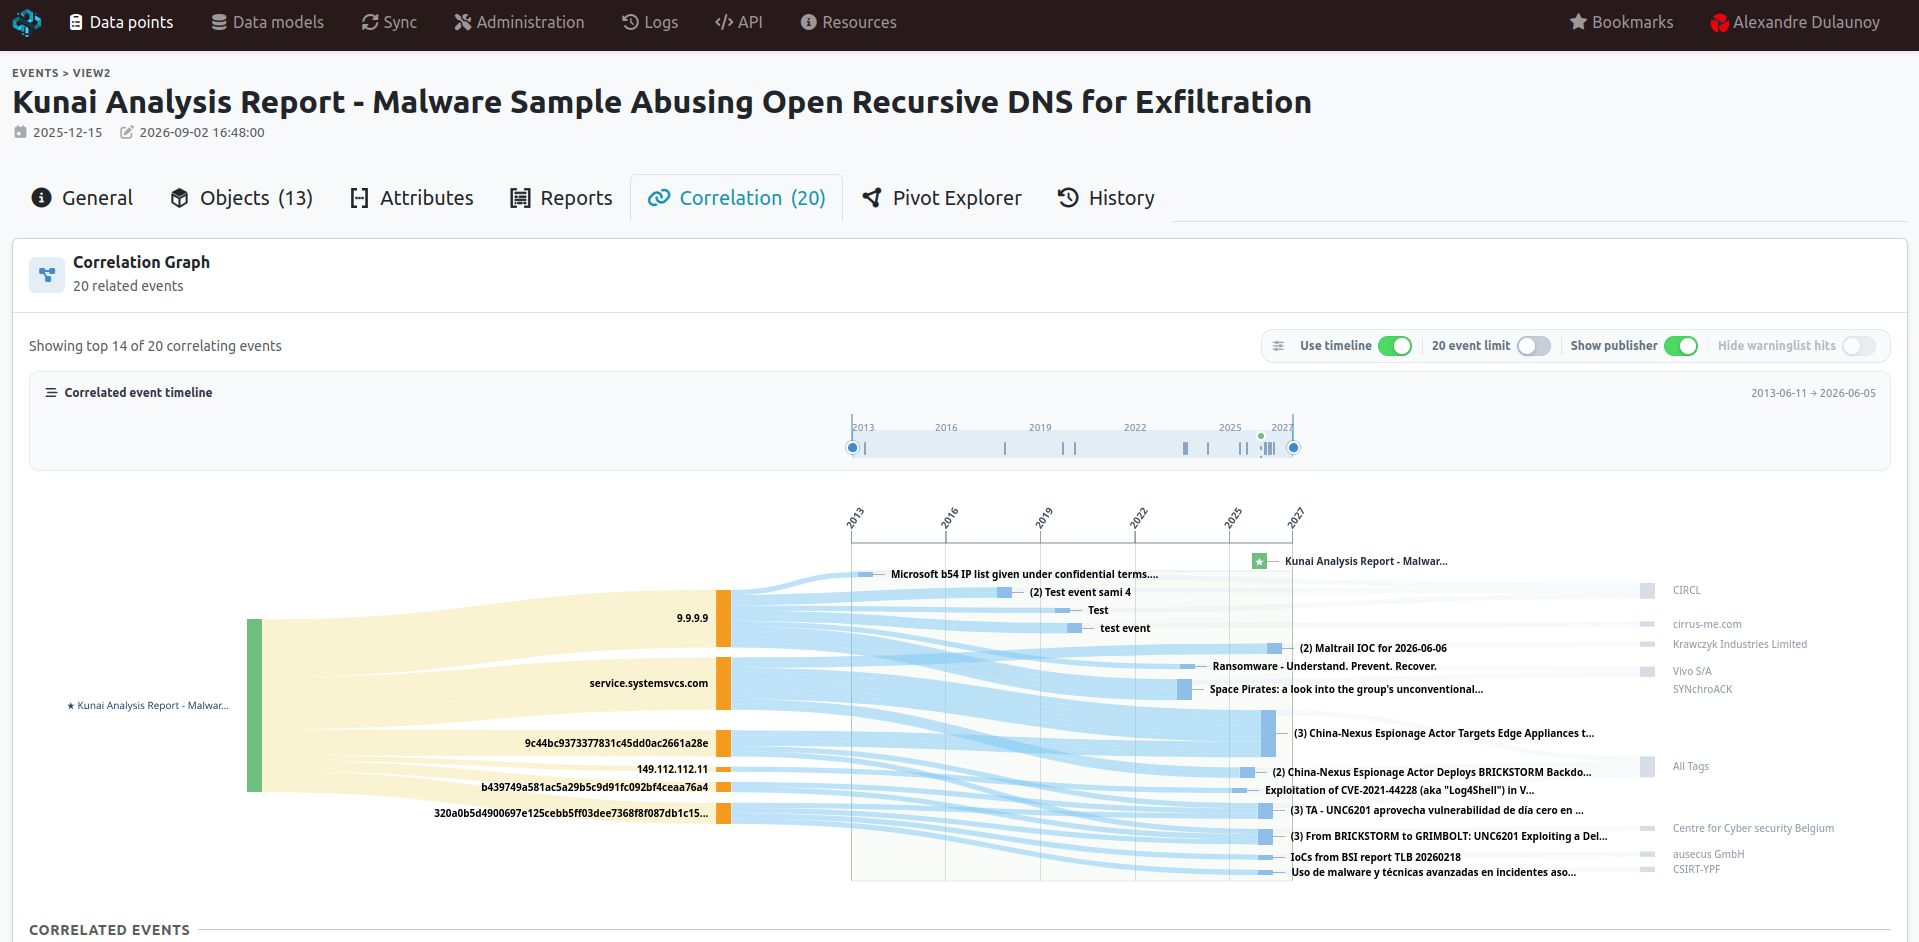
Expands Overmind event quick-action cards with merge attributes, enrich event, contact reporter, delegate publishing, execute ad-hoc workflows, and recorrelate events operations.
 v2.5.46 · Sep 2026
· source
· release history
- Exposes merge attributes, enrich event, contact reporter, delegate publishing, execute ad-hoc workflows, and recorrelate events as quick actions on Event cards in Overmind v2.5.46 · Sep 2026 · source · release history
- Scheduler tasks support manual on-demand triggering via a play button, per-task execution logs, and per-user run context. v2.5.18 · Aug 2025 · source · release history
- Adds ability to run debugged ad-hoc workflows on specific event IDs directly from the Workflow Editor. v2.5.11 · May 2025 · source · release history
- Adds ability to run debugged ad-hoc workflows directly on specific event IDs in the Workflow Editor. v2.4.209 · May 2025 · source · release history
- Adds Ad-Hoc Workflows that run independently of application triggers, executable manually or on a schedule. v2.5.2 · Nov 2024 · source · release history
example
-
Trigger a fresh recorrelation of a specific event after bulk-importing new attributes, without waiting for a scheduled run.
curl -X POST https://<misp-instance>/events/recorrelate/<event_id> -H 'Authorization: <api_key>' -H 'Accept: application/json'v2.5.21 · Sep 2025 · source
Incident case management 1 feature Investigation and response since 2018
Mass-action event tagging verified Allows analysts to apply tags or galaxy clusters to many events at once rather than editing each one individually.
Shared capability: Incident case management
release
- Adds mass-action tagging and galaxy-cluster attachment to multiple selected events at once from the Event index. v2.5.41 · Jun 2026 · source · release history
- Adds mass tagging and galaxy cluster attachment to multiple selected events at once from the event index. v2.5.41 · Jun 2026 · source · release history
- Added mass local cluster tagging option in the [event:view] interface v2.4.183 · Jan 2024 · source · release history
- Updated API tag functions to accept UUIDs in addition to local IDs v2.4.183 · Jan 2024 · source · release history
-
GET /api/attributes/deleteAttributesnow supports mass deletion of attributes via the API v2.4.89 · Mar 2018 · source · release history
example
-
Mass-tag a selection of events from the Event index to rapidly apply a new campaign tag across multiple incidents.
In the Event index, check the checkboxes next to the target events, then choose Mass Actions > Tag Events and select or type the tag to apply across all selected events.v2.5.41 · Jun 2026 · source -
Mass delete multiple attributes in one API call without needing to iterate through them individually.
curl -X GET 'https://<MISP_HOST>/api/attributes/deleteAttributes?uuid=<uuid1>&uuid=<uuid2>' -H 'Authorization: <API_KEY>' -H 'Accept: application/json' -H 'Content-Type: application/json'v2.4.89 · Mar 2018 · source
api 10 total
-
GET /tags/view/{tagId}· source · full API surface -
POST /tags/add· source · full API surface -
POST /events/removeTag/{eventId}/{tagId}· source · full API surface -
GET /tags· source · full API surface -
POST /tags/delete/{tagId}· source · full API surface -
POST /tags/edit/{tagId}· source · full API surface
Forensic timeline analysis 1 feature Investigation and response since 2020
Event timeline editor shipped Provides a timeline viewer and editor per event for visualizing and editing the time-based occurrences of attributes and objects.
Shared capability: Forensic timeline analysis
release
- Adds a timeline viewer/editor per event for visualizing and editing time-based attribute and object occurrences. v2.4.120 · Jan 2020 · source · release history
Static malware analysis 1 feature Investigation and response since 2017
Extended binary import and parsing shipped Enables importing PE, ELF, and Mach-O binaries with automatic object structure creation using PyMISP and LIEF.
Shared capability: Static malware analysis
release
-
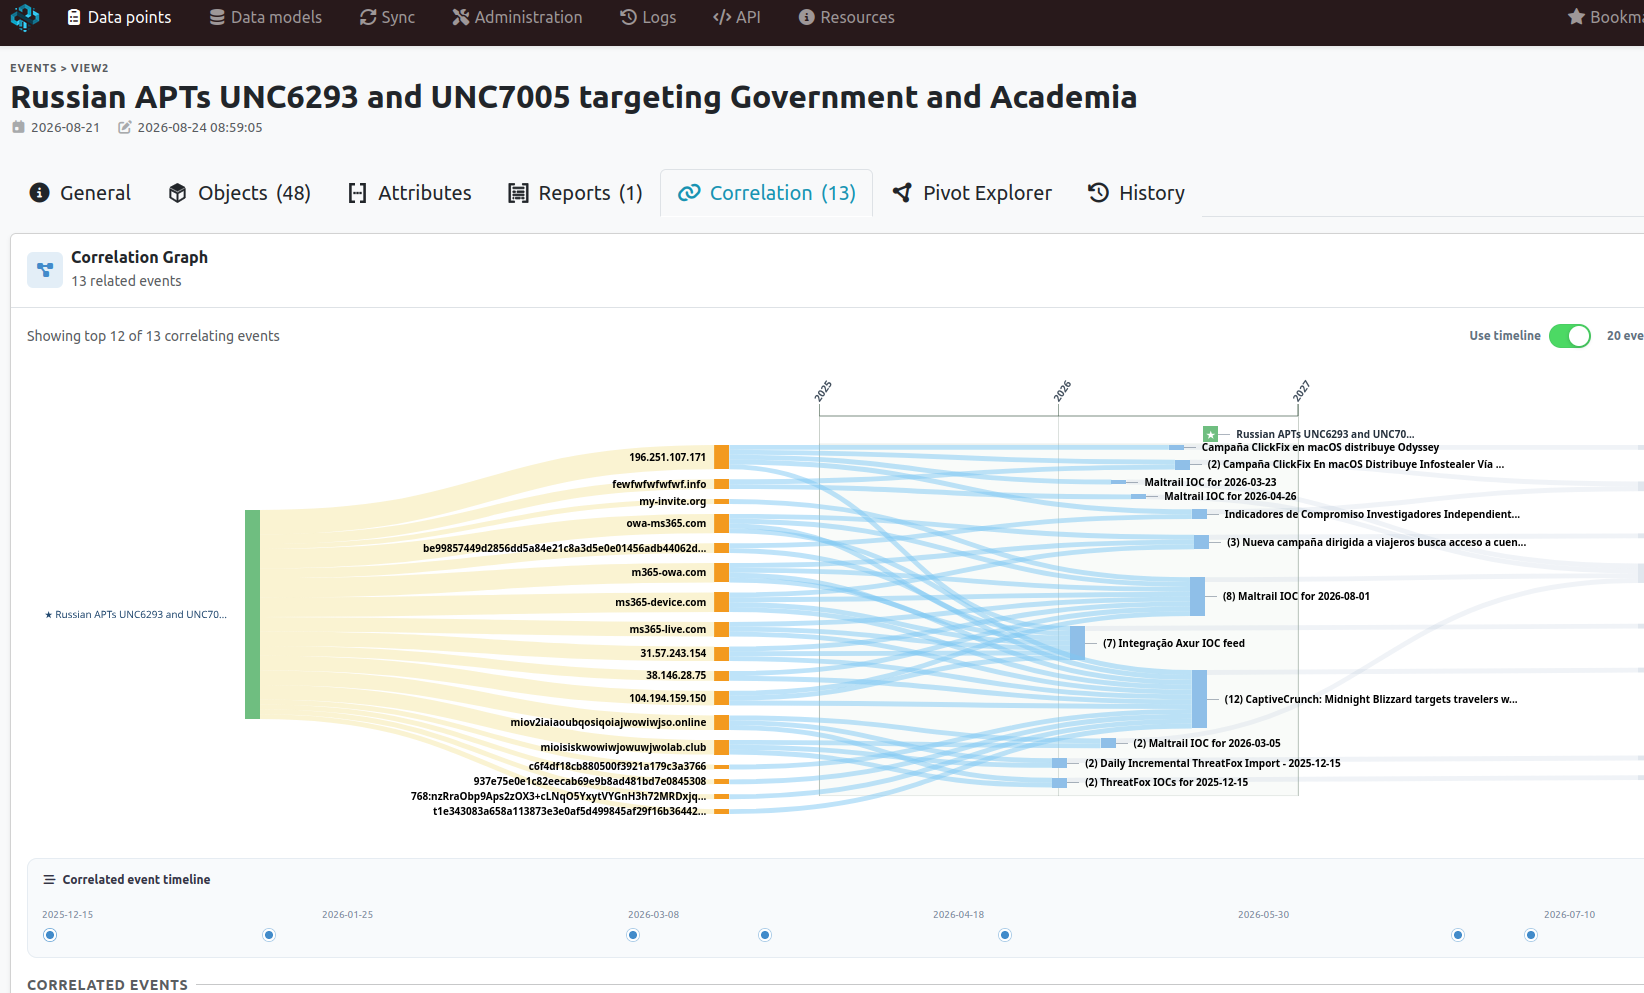
Adds an import action on the event index and server preview views.
 v2.5.45 · Aug 2026
· source
· release history
- Parsing PE binary extensions within File observable objects improved via misp-stix library update v2.4.183 · Jan 2024 · source · release history
- Enables extended file import for binaries (PE, ELF, MachOS) using PyMISP and LIEF to automatically create parsed object structures v2.4.80 · Sep 2017 · source · release history
OIDC SSO 1 feature Identity and access since 2021
OIDC authentication shipped Lets users log in via OpenID Connect, with optional Pushed Authorization Requests for added security.
Shared capability: OIDC SSO
release 18 total
- New option to disable OIDC Pushed Authorization Requests (PAR) for environments that cannot support it. v2.5.42 · Jun 2026 · source · release history
- Adds an option to disable OIDC Pushed Authorization Requests (PAR) for deployments where PAR is unsupported or unwanted. v2.5.42 · Jun 2026 · source · release history
- Supports configurable login button text for OIDC authentication. v2.5.41 · Jun 2026 · source · release history
- Enables configurable login button text for OIDC authentication. v2.5.41 · Jun 2026 · source · release history
- Introduces support for loading authentication plugins dynamically based on configuration settings. v2.5.10 · May 2025 · source · release history
-
Introduces support for loading authentication plugins (e.g.,
OidcAuth) based on configuration settings rather than requiring manual bootstrap code. v2.4.208 · May 2025 · source · release history
example
-
Disable OIDC PAR for an IdP that does not support Pushed Authorization Requests, preventing login failures in those environments.
In the console, go to Server Settings & Maintenance > Plugin Settings > OIDC and set the disable PAR option to true.v2.5.42 · Jun 2026 · source -
Disable OIDC PAR for an identity provider that does not support the Pushed Authorization Request endpoint.
In the MISP UI, go to Server Settings > Plugin > Authentication, find the OIDC settings section, and set the 'Disable PAR' option to true.v2.5.42 · Jun 2026 · source -
Set a custom OIDC login button label so users see your organisation's identity provider name instead of a generic button.
# In app/Config/config.php or equivalent OIDC config block: 'OidcAuth' => [ 'button_text' => 'Login with CorpSSO', ... ]v2.5.41 · Jun 2026 · source -
Enable mixedAuth so users can authenticate via either OIDC or local credentials, with identity provider selection at login.
In the MISP admin console, go to Administration > Server Settings > OIDC and enable `mixedAuth` along with configuring the identity provider selection.v2.4.209 · May 2025 · source
Other / not yet classified 128 features Features we have not matched to a capability yet. A suggested match is marked.
Overmind (Beta) UI verified Provides a modernised Bootstrap 5 interface that progressively replaces legacy views across events, logs, galaxies, and other core areas.
release 35 total
- Adds warninglist match indicators next to attributes in Overmind views. v2.5.50 · Oct 2026 · source · release history
-
Adds a collection card and *add to collection* action to the Overmind event view.
 v2.5.47 · Sep 2026
· source
· release history
- Adds a new More filters expandable section to the users, servers, organisations, workflows, logs, galaxy clusters, collections, and event attribute indexes in Overmind. v2.5.47 · Sep 2026 · source · release history
- Adds a JSON field component to Overmind forms, used by the decaying model modal. v2.5.47 · Sep 2026 · source · release history
-
Enables server-specific card views in the Overmind UI for event indexes
v2.5.46 · Sep 2026
· source
· release history
- Adds responsive correlation graph timelines and collapses correlated events by default in Overmind. v2.5.46 · Sep 2026 · source · release history
example
-
Enable the Overmind UI development preview to access the new migrated views including Event Templates and Correlation Graph.
In the MISP web UI, go to Administration > Server Settings & Maintenance > Simple Settings, find the theme selector, and set it to Overmind.v2.5.37 · Apr 2026 · source -
Use the new decomposed event view endpoints and mass-select actions in the Event Index via the Overmind UI.
In the console, go to Administration > Server Settings > MISP > enable theming, set the theme to the Overmind/EventTest theme, then navigate to an event to load attributes, objects, related events,…v2.5.35 · Mar 2026 · source -
Enable the new theme system so users can switch to Overmind or BetaUI in their profile settings.
/var/www/MISP/app/Console/cake Admin setSetting "MISP.enable_themes" 1v2.5.33 · Mar 2026 · source -
Enable the new beta UI/UX mode to get the redesigned Event Index and navigation — useful for evaluating the next-generation interface before it becomes the default.
In the MISP UI, go to your User Settings and enable the beta UI / UX mode option.v2.5.30 · Dec 2025 · source
api 41 total
-
GET /taxonomies/view/{taxonomyId}· source · full API surface -
GET /events/view/{eventId}· source · full API surface -
PUT /admin/users/edit/{userId}· source · full API surface -
POST /eventReports/edit/{eventReportId}· source · full API surface -
POST /taxonomies/update· source · full API surface -
GET /admin/users· source · full API surface
Server synchronisation verified Keeps events, tags, and collections in sync between MISP instances by pulling from or pushing to peer servers.
release 33 total
-
Adds collection synchronisation between MISP instances in both pull and push directions, with per-server
pull_collections/push_collectionstoggles, feature negotiation with pagination, and acollections.lockedorigin-protection flag. v2.5.43 · Jul 2026 · source · release history - Reduces sync overhead by requesting only the event-tags fingerprint instead of the full tag list. v2.5.41 · Jun 2026 · source · release history
-
New client-side caching endpoint for synchronization bypasses heavy
restSearchlogic, reducing memory footprint and speeding up large-instance sync. v2.5.33 · Mar 2026 · source · release history - Sync users can now update sharing groups they can see and push updates via different sync connections than the original source. v2.5.31 · Dec 2025 · source · release history
- Adds warning logging for remote server version mismatches during sync. v2.5.10 · May 2025 · source · release history
-
New
perm_sync_internalpermission flag allows internal pulls without distribution downgrade, letting the remote instance control downgrade logic. v2.4.206 · Mar 2025 · source · release history
example 9 total
-
Enable collection push to a remote peer so newly created collections are automatically synchronised to that instance.
In the MISP UI, go to Sync Actions > List Servers, edit the target server, and enable the push_collections and pull_collections toggles under the synchronisation options.v2.5.43 · Jul 2026 · source -
Enable collection sync to a remote MISP peer so your local collections are pushed to and pulled from that instance automatically.
In the MISP UI, go to Sync Actions > List Servers, edit the target server, and enable the pull_collections and push_collections toggles.v2.5.43 · Jul 2026 · source -
Test a sync connection and immediately see how many events would be pulled, helping you validate sync rules before committing.
In the MISP UI, go to Administration > Servers, select a remote server, and click 'Test' — the result now includes the count of events that would be synced under the current sync rules.v2.4.206 · Mar 2025 · source -
Pull events from a remote instance marked as an internal instance without having their distribution level downgraded, provided the remote user has
perm_sync_internal.In the MISP UI, go to Administration > Servers, edit the remote server, and ensure the remote sync user has the `perm_sync_internal` permission — the pulling instance will then preserve distribution…v2.4.206 · Mar 2025 · source -
Allow a remote MISP instance's internal-distribution events to be pulled without distribution downgrade, by granting the remote sync user the perm_sync_internal permission.
In the MISP UI, go to Administration > List Users, edit the remote sync user, and enable the `perm_sync_internal` permission under Role settings.v2.5.8 · Mar 2025 · source -
Validate how many events your current sync rules would filter before pushing to a remote MISP instance — navigate to the sync server settings and use the new widget.
In the MISP UI, go to Sync Actions > List Servers, open a server entry, and use the new 'Test Sync Rules' widget to see the count of events that would be filtered by the configured synchronization…v2.5.7 · Feb 2025 · source
api 12 total
-
POST /servers/import· source · full API surface -
GET /servers/getVersion· source · full API surface -
POST /servers/add· source · full API surface -
GET /servers/pull/{serverId}/{pullTechnique}· source · full API surface -
GET /servers· source · full API surface -
PUT /servers/edit/{serverId}· source · full API surface
Threat intelligence feeds verified Enables users to pull in external OSINT and threat-intelligence feeds to enrich the local instance with indicator data from the wider community.
release 31 total
- Adds the phishunt.io feed of active phishing URLs as a new built-in feed. v2.5.50 · Oct 2026 · source · release history
-
Adds TweetFeed and several Threatbase feeds to the default MISP feed list.
v2.5.47 · Sep 2026
· source
· release history
- Adds HoneyLabs default feeds covering active exploiters and malware infrastructure. v2.5.43 · Jul 2026 · source · release history
- Adds SiberKapan (Turkey-focused threat-intel platform) to the default feeds. v2.5.42 · Jun 2026 · source · release history
- Adds SiberKapan (Turkey-focused threat-intelligence platform) to the default MISP feeds list. v2.5.42 · Jun 2026 · source · release history
- Adds two new default threat intelligence feeds: PrecisionSec OSINT Threat Intelligence and Rectifyq MISP Feeds. v2.5.41 · Jun 2026 · source · release history
docs
- Open source threat intelligence sharing platform for collecting, storing, and distributing cybersecurity indicators, threats, and malware analysis data.
example
-
Pull in the new NOCACTI feeds via the MISP UI after upgrading to start ingesting adversary infrastructure and intrusion indicators.
In the console, go to Sync Actions > Feeds, find the NOCACTI Adversary Infrastructure and NOCACTI Intrusion feeds in the feed list, enable them, then click Fetch and store all feed data.v2.5.31 · Dec 2025 · source -
Set up a recurring feed-fetch task so MISP automatically pulls all feeds on a schedule without external cron jobs.
Navigate to https://YOUR_MISP_HOST/tasks, click 'Add Task', select action type 'Fetch' under 'Feeds', choose 'All' feeds, set your recurrence interval, save, then enable the task.v2.5.18 · Aug 2025 · source -
Add a new Greynoise IP object to an event for immediate enrichment integration.
In the Event view > Objects tab, click 'Add Object' and select 'Greynoise-ip'.v2.4.170 · Apr 2023 · source -
Compare a new feed to existing ones to verify coverage before ingestion.
Use the 'New overlap feed comparator' in the UIv2.4.104 · Mar 2019 · source
api 16 total
-
POST /warninglists/checkValue· source · full API surface -
POST /feeds/cacheFeeds/{cacheFeedsScope}· source · full API surface -
POST /warninglists/update· source · full API surface -
POST /servers/cache· source · full API surface -
GET /feeds/view/{feedId}· source · full API surface -
POST /feeds/fetchFromFeed/{feedId}· source · full API surface
Built-in graphical workflow system shipped Provides a module-based interface for customizing automated tasks such as event publishing, user enrollment, and synchronization logic.
release 43 total
- New Workflows Blocklist action module writes event attributes to a blocklist file, with removal-by-tag, atomic writes with one-generation backup, and optional rolling filesystem snapshots. v2.5.38 · May 2026 · source · release history
-
Ad-hoc workflows now support passing in environment variables and capturing module-returned data under
_env.misp_module_resultsfor use by downstream nodes. v2.5.37 · Apr 2026 · source · release history -
New
analyst-data:after-saveworkflow trigger added. v2.5.37 · Apr 2026 · source · release history - New settings to gate arbitrary URLs in event reports and workflows, controlling SSRF attack surface. v2.5.33 · Mar 2026 · source · release history
-
Workflow modules
threat-level-ifandaggregate-ifreceive new enhancements. v2.5.33 · Mar 2026 · source · release history - New Timestamp Filter workflow module enabling filtering of events based on timestamp values. v2.5.32 · Jan 2026 · source · release history
example
-
Enable the new Blocklist action module in a workflow to automatically write matched event attributes to a blocklist file, grouped by tag.
In the MISP UI, go to Event Actions > Workflows, open or create a workflow, and add the 'Blocklist' action module from the module palette.v2.5.38 · May 2026 · source -
Act on event deletions in a workflow — e.g., to notify an external system or log deletions before they occur.
In the MISP console, go to Event Actions > Workflows, create a new workflow, and add the `trigger-event-before-delete` trigger as the starting node.v2.5.32 · Jan 2026 · source -
Explore the built-in workflow system to customize automated tasks like event publishing.
In the MISP UI, navigate to the new 'Workflows' section to access the graphical interface for defining custom logical steps in your synchronization and enrollment processes.v2.4.160 · Aug 2022 · source
Analyst dashboard verified Gives analysts a configurable home dashboard with widgets covering trending threats, KPIs, ATT&CK heatmaps, and correlation views.
release 33 total
- ATT&CK dashboard widget (AttackWidget) now counts techniques via an ACL-aware Event find, ensuring results respect user permissions. v2.5.40 · Jun 2026 · source · release history
- New analyst-focused dashboard widgets: trending vulnerabilities, threat actors, and ATT&CK techniques; new-data KPI cards; event cards; recent event reports; recent analyst notes and opinions; recent local galaxy clusters; and 'overlap with my org' correlation-based views. v2.5.39 · Jun 2026 · source · release history
-
New
misp-iconifyicon set used for dashboard stat glyphs. v2.5.39 · Jun 2026 · source · release history - New analyst dashboard widgets: trending vulnerabilities, threat actors, and ATT&CK techniques; new-data KPI cards; event cards; recent event reports; recent analyst notes and opinions; recent local galaxy clusters; and 'overlap with my org' correlation views. v2.5.39 · Jun 2026 · source · release history
-
Dashboard widgets gain typed configuration controls for dimensions, country/sector filters,
exclude_own_org, event stream filters, and galaxy type filtering. v2.5.39 · Jun 2026 · source · release history - Live light/dark dashboard theme switching — including chart retheming — with persisted user preference and no-flash boot. v2.5.39 · Jun 2026 · source · release history
example 8 total
-
Enable a trending threat actors widget on your analyst dashboard to surface the most-referenced actors across recent events.
In the MISP dashboard, click Add Widget > select 'Trending threat actors' > configure the country/sector filters and `exclude_own_org` toggle > click Save.v2.5.39 · Jun 2026 · source -
Switch your dashboard to dark theme so SOC analysts working night shifts get a low-glare view that persists across sessions.
In the MISP dashboard header, click the theme toggle (sun/moon icon) to switch between light and dark mode — the preference is saved to your user profile and charts retheme live.v2.5.39 · Jun 2026 · source -
Switch the dashboard between light and dark themes without a page reload to match analyst environment preferences.
In the MISP dashboard, click the theme toggle control; the dashboard and all charts retheme live and the preference is persisted for your user account.v2.5.39 · Jun 2026 · source -
Enable the 'overlap with my org' correlation widget to surface events sharing indicators with your organisation's data.
In the dashboard, go to the widget picker, select 'Overlap with my org', configure country/sector filters and `exclude_own_org` as needed, then save the layout.v2.5.39 · Jun 2026 · source -
Enable themes on a Docker-based MISP installation to let users experiment with the new UIs.
docker exec -it misp-docker-misp-core-1 /var/www/MISP/app/Console/cake Admin setSetting "MISP.enable_themes" 1v2.5.33 · Mar 2026 · source -
View threat hunting coverage using the new ATT&CK visualization on the dashboard.
Navigate to Dashboard > Widgets > Add Widget > 'ATT&CK heatmap'v2.4.173 · Jul 2023 · source
api
-
GET /attributes/attributeStatistics/{context}/{percentage}· source · full API surface
Galaxy cluster management verified Lets authorised users create, publish, and share galaxy clusters that classify and contextualise threat actors, techniques, and other entities.
Also counts toward: REST API
release 18 total
- Requires publish permission to publish galaxy clusters, enforcing stricter access control on cluster publication. v2.5.39 · Jun 2026 · source · release history
- Required publish permission enforced for publishing galaxy clusters. v2.5.39 · Jun 2026 · source · release history
- Galaxy view now displays the count of attributes linked to each galaxy cluster. v2.5.15 · Jun 2025 · source · release history
- Galaxy view now displays a count of attributes linked to each galaxy cluster. v2.4.213 · Jun 2025 · source · release history
- Adds a new default distribution setting for galaxies. v2.5.8 · Mar 2025 · source · release history
- Adds new default distribution setting for galaxies. v2.4.206 · Mar 2025 · source · release history
example
-
Export a finished Event Report as a properly formatted PDF for sharing outside MISP.
Open the Event Report, click the Download menu, and select 'Download as PDF' (requires the `convert_markdown_to_pdf.py` misp-module and its dependencies: Pandoc, wkhtmltopdf, mermaid-cli).v2.5.2 · Nov 2024 · source -
Export a finished Event Report as a polished PDF for stakeholder distribution, using Pandoc rather than the browser print dialog.
Open the Event Report, click the download icon and select 'Download as PDF' — requires `convert_markdown_to_pdf.py` from misp-modules and Pandoc, wkhtmltopdf, and mermaid-cli installed on the MISP…v2.4.200 · Nov 2024 · source -
Query galaxy cluster metadata fields via restSearch to find attributes linked to specific suspected victims
curl -X POST 'https://<misp>/attributes/restsearch' \ -H 'Authorization: <auth>' \ -H 'Content-Type: application/json' \ -d '{ "galaxy.cfr-suspected-victims": ["China", "Japan"] }'v2.4.118 · Nov 2019 · source -
Use the newly added ICS/OT taxonomy to tag indicators
When creating or editing an indicator, select 'ics' from the available taxonomy tags.v2.4.114 · Aug 2019 · source
api 17 total
-
POST /galaxies/update· source · full API surface -
POST /galaxy_clusters/unpublish/{galaxyClusterId}· source · full API surface -
DELETE /galaxies/delete/{galaxyId}· source · full API surface -
PUT /galaxy_clusters/edit/{galaxyClusterId}· source · full API surface -
POST /galaxies/import· source · full API surface -
POST /galaxies/attachCluster/{attachTargetId}/{attachTargetType}/local:{local}· source · full API surface
Server settings management verified Gives administrators a unified interface to view and change all instance configuration settings, including those normally hidden or CLI-only.
Also counts toward: REST API, Web management console
release 21 total
-
Restricts
download_attachments_on_loadsetting to CLI-only configuration, removing it from the web interface and API. v2.5.50 · Oct 2026 · source · release history -
Adds
MISP.redis_host,Plugin.ZeroMQ_redis_host, andSimpleBackgroundJobs.redis_hostsettings as CLI-only — these can no longer be changed through the web interface or API, reducing risk from a compromised admin session. v2.5.50 · Oct 2026 · source · release history -
Adds
/gpg.ascendpoint to serve the instance GPG key with caching
v2.5.45 · Aug 2026
· source
· release history
-
Serves the instance GPG key at
/gpg.ascwith caching. v2.5.45 · Aug 2026 · source · release history - Supports environment variables as a third settings source alongside config file and database, enabling cleaner containerised and IaC deployments. v2.5.43 · Jul 2026 · source · release history
- Supports environment variables as a third settings source alongside config file and database, enabling cleaner containerised and infrastructure-as-code deployments. v2.5.43 · Jul 2026 · source · release history
example
-
Retrieve all current server settings via the CLI to audit configuration.
/var/www/MISP/app/Console/cake Admin getSettingv2.4.90 · Apr 2018 · source
api 11 total
-
GET /user_settings· source · full API surface -
GET /organisations· source · full API surface -
POST /servers/serverSettingsEdit/{settingName}· source · full API surface -
POST /user_settings· source · full API surface -
POST /admin/logs· source · full API surface -
DELETE /user_settings/delete/{userSettingId}· source · full API surface
STIX import and export shipped Converts MISP events to and from STIX format, preserving TLP markings and producing consistent output.
release 25 total
- Updated STIX engine (misp-stix 2026.6.1) adds full TLP marking support across import and export paths, expanded patterning-language support, more deterministic byte-stable conversions, and regenerated mapping documentation. v2.5.39 · Jun 2026 · source · release history
-
Updated
misp-stix 2026.6.1brings full TLP marking support shared across import and export paths, expanded patterning-language support, more deterministic byte-stable conversions, and regenerated mapping documentation. v2.5.39 · Jun 2026 · source · release history -
STIX 2 export now defaults to version 2.1 and adds a new library entry point for exporting MISP Object collections to STIX 2.x, switching from MISP's custom
cti-python-stix2fork to the upstream library bundled withmisp-stix. v2.5.37 · Apr 2026 · source · release history - Updates MISP-STIX to include indicator and observable fingerprinting capabilities. v2.5.35 · Mar 2026 · source · release history
- Updates misp-stix with better STIX 2 input handling to tolerate invalid STIX 2 output from non-compliant TIP platforms. v2.5.26 · Nov 2025 · source · release history
-
Adds support for
misp_stix_converterinstixtest.pyfor improved STIX testing. v2.5.5 · Jan 2025 · source · release history
example
-
Export attributes from a specific search query in STIX 2 format via the API.
curl -k -H 'Authorization: <YOUR_API_KEY>' -H 'Accept: application/json' 'https://<MISP_HOST>/attributes/restSearch?returntype=stix2&search=<your_search_criteria>'v2.4.152 · Dec 2021 · source -
Import external STIX 2.0 threat intel data directly into a MISP event without using the command line or Python scripts.
In the MISP web UI, navigate to 'Events' > 'Add Event', select the 'Import' tab, choose 'STIX 2.0' as the format, upload the file or paste the content, and submit.v2.4.89 · Mar 2018 · source -
Import a STIX 1.1.1 XML file directly from the MISP web interface to ingest external threat intel.
Navigate to Events > Add Event > Import and select 'STIX 1.1.1 XML' as the format.v2.4.88 · Feb 2018 · source
Event Reports shipped Allows users to attach structured Markdown reports containing attributes, objects, galaxies, and tags to events.
release 22 total
-
Adds an add button on the Overmind event reports tab and an improved markdown editor for event report previews.
v2.5.47 · Sep 2026
· source
· release history
- Event reports can now be looked up by UUID. v2.4.211 · Jun 2025 · source · release history
-
Adds a
placeholderplugin to the CodeMirror editor interface. v2.4.201 · Dec 2024 · source · release history - Introduces instance-wide template variables for reports, manageable only by site administrators but viewable and usable by all users. v2.4.201 · Dec 2024 · source · release history
- Introduces instance-wide template variables for reports, manageable only by site administrators but viewable and usable by all users. v2.5.3 · Dec 2024 · source · release history
-
Template variables defined in user-settings are now supported in Event Reports using
{{ var_name }}handlebars-style notation, substituted automatically on visualisation or export. v2.4.200 · Nov 2024 · source · release history
example
-
Enable instance-wide report template variables so all analysts can reference shared context (e.g., CERT name, TLP defaults) in every event report without per-report duplication.
In the MISP console, go to Administration > Report Variables and create a new instance-wide variable (requires site administrator role).v2.5.3 · Dec 2024 · source -
Create an instance-wide report template variable as a site admin so all users can reference it in event reports.
In the MISP UI, go to Administration > Report Variables and create a new instance-wide variable; it will be visible and usable by all users in event reports.v2.4.201 · Dec 2024 · source -
Reuse analyst-specific boilerplate (e.g. analyst name, TLP caveat) across all Event Reports without retyping.
In your user profile settings, define a template variable (e.g. `analyst_name = Jane Doe`), then reference it inside any Event Report as `{{ analyst_name }}` — it will be substituted automatically…v2.4.200 · Nov 2024 · source -
Attach a markdown report to an event using the new editor.
In the MISP UI, navigate to an Event > click 'Add Report' to open the Markdown editor.v2.4.133 · Oct 2020 · source
API key (authkey) management verified Manages per-user API keys, controlling how each user or integration authenticates against the MISP API.
Also counts toward: REST API
release 16 total
-
The
unique_ipsfield on authkeys is now derive-only and can no longer be seeded on key creation; any tooling or scripts that setunique_ipsat key-creation time will have that value ignored or rejected. v2.5.42 · Jun 2026 · source · release history -
X-MISP-AUTHheader added as an alternative to Authorization for API requests. v2.4.180 · Dec 2023 · source · release history -
New CLI command to expire active
AuthKeysmissing an IP allowlist v2.4.177 · Sep 2023 · source · release history -
Adds
authkeyssetting to mandate IP allowlist for advanced authentication keys. v2.4.174 · Jul 2023 · source · release history - Enables org admins to manage authentication keys directly via the interface or API. v2.4.157 · Mar 2022 · source · release history
- Adds support for creating read-only authentication keys via the API (requires enabling advanced authentication key feature). v2.4.146 · Jul 2021 · source · release history
example
-
Authenticate to the MISP API using the new
X-MISP-AUTHheader instead of the standard Authorization header.curl -H 'X-MISP-AUTH: <your_api_key>' https://misp.example.com/attributes/restSearchv2.4.180 · Dec 2023 · source -
Pin an API key to a specific IP address for tighter security controls in the UI.
In the User > My settings > Auth tab, select 'Pin IP' next to the desired API key entry and save.v2.4.170 · Apr 2023 · source -
Reset all synchronization user API keys across the instance via the CLI.
/var/www/MISP/app/Console/cake resetSyncAuthkeysv2.4.115 · Sep 2019 · source
api 7 total
-
POST /auth_keys/edit/{authKeyId}· source · full API surface -
GET /auth_keys· source · full API surface -
GET /auth_keys/view/{authKeyId}· source · full API surface -
POST /auth_keys· source · full API surface -
POST /auth_keys/add/{userId}· source · full API surface -
DELETE /users/totp_delete/{userId}· source · full API surface
Event correlation graph verified Displays relationships between attributes and objects as an interactive graph, letting analysts explore connections and edit references visually.
Also counts toward: REST API
release 10 total
- Introduces Pivotick as an early-stage drop-in replacement for the legacy event graph, including a draft drag-and-drop reference editor. v2.5.43 · Jul 2026 · source · release history
- Introduces Pivotick as an initial drop-in replacement for the legacy event graph, including a draft drag-and-drop reference editor. v2.5.43 · Jul 2026 · source · release history
- Integrates the correlation graph into the Overmind/Insight UI. v2.5.42 · Jun 2026 · source · release history
- Overmind UI gains full coverage for Tags, Tag Collections, Taxonomies, Templates, Object Templates, Object Relationships, REST Client, Automation & Export Views, Correlation Graph (rewritten in vanilla JS), and Event Templates. v2.5.37 · Apr 2026 · source · release history
-
Improves correlation engine performance by splitting attribute correlation lookups into two distinct queries on
value1andvalue2for optimized MySQL performance. v2.5.6 · Jan 2025 · source · release history -
Adds
show_server_correlations_for_all_usersconfiguration option to allow non-privileged users to view server correlations. v2.4.182 · Dec 2023 · source · release history
example
-
Visualize connections between objects and attributes within a MISP event to analyze relationships and edit data graphically.
In the MISP web UI, open an existing Event, click on the 'Graph' tab to launch the new event graph editor.v2.4.89 · Mar 2018 · source
api 12 total
-
POST /objects/restsearch· source · full API surface -
POST /attributes/restore/{attributeId}· source · full API surface -
GET /attributes/getAttributeByB64Value/{base64Value}· source · full API surface -
DELETE /objects/delete/{objectId}/{hardDelete}· source · full API surface -
POST /attributes/add/{eventId}· source · full API surface -
POST /attributes/restSearch· source · full API surface
Collection management verified Lets users group MISP objects into named collections that can be shared and kept in sync across instances.
Also counts toward: REST API
release
-
Adds collection synchronisation between MISP instances in both pull and push directions, with per-server
pull_collections/push_collectionstoggles, feature negotiation with pagination, and acollections.lockedorigin-protection flag. v2.5.43 · Jul 2026 · source · release history -
Enables collection synchronisation between MISP instances in both pull and push directions, with per-server
pull_collections/push_collectionstoggles, paginated feature negotiation, and acollections.lockedorigin-protection flag mirroring galaxy cluster handling. v2.5.43 · Jul 2026 · source · release history - Enables editing, viewing, and deletion of Collections by UUID. v2.5.11 · May 2025 · source · release history
- Enables editing, viewing, and deletion of Collections by UUID. v2.4.209 · May 2025 · source · release history
example
-
Manage a collection by UUID — useful when you don't have the numeric ID available (e.g., cross-instance references).
GET /collections/view/<uuid>v2.5.11 · May 2025 · source
api 17 total
-
DELETE /collections/delete/{collectionId}· source · full API surface -
POST /collections/edit/{collectionId}· source · full API surface -
POST /sharing_groups/addServer/{sharingGroupId}/{serverId}· source · full API surface -
POST /sharing_group_blueprints/add· source · full API surface -
POST /collections/index/{filter}· source · full API surface -
GET /sharing_group_blueprints/view/{sharingGroupBlueprintId}· source · full API surface
Search performance and diagnostic monitoring shipped Optimizes search operations through Redis-backed pagination, POST request support for complex queries, and parallel processing to allow multiple independent search tabs.
previously: Search performance enhancements
Also counts toward: REST API
release 18 total
-
Switches
restsearchto cursor-based pagination, eliminating performance degradation on deep pagination of large attribute datasets. v2.5.35 · Mar 2026 · source · release history - Introduces a new correlation dispatcher enabling per-page correlation loading instead of loading all correlations for an entire event at once. v2.5.35 · Mar 2026 · source · release history
- Adds new AJAX endpoints (view2(), viewAttributes(), viewObjects(), viewRelatedEvents(), viewWarninglistHits()) that decompose the monolithic event view into asynchronously loaded components for faster rendering. v2.5.35 · Mar 2026 · source · release history
-
New
/attributes/getAttributeByB64Valueendpoint enables efficient attribute lookups by Base64 value. v2.5.33 · Mar 2026 · source · release history - Redesigns top navigation bar with reorganized clustering and fly-out menus in the new beta mode. v2.5.30 · Dec 2025 · source · release history
- New dedicated endpoint for organization logo loading uses cached images instead of live base64 decoding, significantly speeding up Event Index rendering. v2.5.30 · Dec 2025 · source · release history
example
-
View slow SQL queries from the Diagnostic controller to identify performance bottlenecks.
GET /diagnostic/slowSqlv2.4.214 · Jul 2025 · source -
Apply high-performance database indexes to events and attributes to speed up queries on large instances.
cake Admin runDBScript highPerformancev2.4.214 · Jul 2025 · source -
Apply high-performance database indexes on a large MISP instance to speed up event/attribute queries and correlations.
cake Admin runDBScript highPerformancev2.5.16 · Jul 2025 · source
Activity auditing and logging shipped Provides mechanisms for logging MISP activities, including an ElasticSearch plugin integration for comprehensive activity audit logs.
Also counts toward: Administrative audit log, SIEM forwarding
release 15 total
- New option to emit syslog messages in JSON format for structured logging and easier downstream processing. v2.5.26 · Nov 2025 · source · release history
- Error logs can now be generated in NDJSON format for easier parsing and integration with modern logging pipelines. v2.5.16 · Jul 2025 · source · release history
-
New
cake Admin runDBScript indexLogscommand adds indexes to the log table for rapid log searching and auditing. v2.5.16 · Jul 2025 · source · release history -
Introduces
userIPand IPUser tools in the user controller for IP-based user lookups. v2.4.209 · May 2025 · source · release history -
Adds new
userIPand IPUser tools to the user controller for IP-based user lookups. v2.5.11 · May 2025 · source · release history -
Adds AuditLog filtering support for
SharingGroupOrgandSharingGroupBlueprintoptions, enabling more targeted audit trail queries. v2.4.204 · Jan 2025 · source · release history
example
-
Add indexes to the log table so audit log searches return results quickly on busy instances.
cake Admin runDBScript indexLogsv2.5.16 · Jul 2025 · source -
Use the reworked Log Search UI to filter and paginate through audit logs without losing your filter state between pages.
In the MISP UI, go to Audit > Search Logs, apply your filters (e.g., by action or model), and navigate pages — filters now persist across pagination.v2.4.203 · Jan 2025 · source
Async background job execution verified Runs long-running operations as background jobs so the user's request returns immediately without waiting.
Also counts toward: REST API
release 9 total
-
Enables managing Supervisor-backed workers directly from the CLI.
v2.5.45 · Aug 2026
· source
· release history
-
Enables async background-job updates via
/servers/updateJSON. v2.5.41 · Jun 2026 · source · release history -
Adds async background-job support to the
/servers/updateJSON endpoint. v2.5.41 · Jun 2026 · source · release history - Switches default worker engine to Supervisor-based implementation for new installs and upgrades, replacing the CakeResque-based engine with a more reliable and lightweight alternative. v2.5.0 · Oct 2024 · source · release history
- The previous correlation engine is retired and replaced; upgrading will regenerate all correlations using the new engine, a process that may take an extended period on large instances. v2.4.160 · Aug 2022 · source · release history
- Two new correlation engines replace the deprecated engine, significantly improving performance and reducing storage requirements v2.4.160 · Aug 2022 · source · release history
example
-
Trigger a background async update of MISP's JSON definitions without blocking the request — useful for automation pipelines.
curl -s -H 'Authorization: <your-api-key>' -H 'Accept: application/json' -H 'Content-Type: application/json' -X POST https://<misp-instance>/servers/updateJSON -d '{"background": true}'v2.5.41 · Jun 2026 · source
api
-
POST /servers/stopWorker/{workerPid}· source · full API surface -
POST /servers/restartDeadWorkers· source · full API surface -
POST /servers/restartWorkers· source · full API surface -
POST /servers/startWorker/{workerType}· source · full API surface -
GET /servers/getWorkers· source · full API surface
Expanded MISP Object and Galaxy templates shipped Adds new object types (e.g., typosquatting, ransomware groups, registry keys, Greynoise) and galaxy clusters (Sigma, DNS abuse) to enrich threat intelligence data.
release 14 total
-
Adds a new MITRE ATLAS Case Study galaxy and updates MITRE ATLAS to the 2026.08 release in misp-galaxy.
v2.5.47 · Sep 2026
· source
· release history
- New misp-galaxy galaxies added: SPARTA, MITRE Fraud Framework, VERIS framework, RMM tools, operating systems, IT-equipment types, software vendors, and taxonomy of fraud. v2.5.37 · Apr 2026 · source · release history
-
New misp-objects templates added:
rulezet-bundle,ruleset-metadata,dga-domain,drone-RID-observation,contact-list,fbi-most-wanted,terminal-output,malicious-website,exif,software,service,container,physical-object,item,mfa-auth. v2.5.37 · Apr 2026 · source · release history - MITRE Atlas framework added to MISP Galaxy as Attack Pattern and Course of Action clusters v2.4.183 · Jan 2024 · source · release history
- New flowintel CM object type available for MISP Objects v2.4.183 · Jan 2024 · source · release history
- Adds SigMF object templates for Signal Metadata Format Specification support. v2.4.175 · Aug 2023 · source · release history
Attack-flow globe visualisation shipped Plots attack-flow data on an interactive 3-D globe so analysts can see geographic patterns in campaign activity.
release 12 total
- Adds WebGL globe visualization for attack-flow data, with selectable globe skins and idle auto-rotation. v2.5.39 · Jun 2026 · source · release history
- WebGL globe support for attack-flow visualizations, with selectable globe skins and idle auto-rotation. v2.5.39 · Jun 2026 · source · release history
- Adds accuracy-radius visualisation for geolocation objects, displayed as a toggleable circle on the map. v2.5.36 · Apr 2026 · source · release history
- Adds native GeoJSON rendering, enabling complex geographic shapes and features to be displayed on maps. v2.5.36 · Apr 2026 · source · release history
-
Adds configurable tile server support via
Plugin.Geolocation_url(defaults tohttps://geo.circl.lu). v2.5.36 · Apr 2026 · source · release history -
Adds interactive geolocation map rendering for objects with geographic coordinates directly in the event view, enabled via
Plugin.Geolocation_enabled. v2.5.36 · Apr 2026 · source · release history
example
-
Enable geolocation map visualisation for events containing geographic objects, pointing to a self-hosted tile server.
app/Console/cake Admin setSetting Plugin.Geolocation_enabled true app/Console/cake Admin setSetting Plugin.Geolocation_url "https://tiles.example.com"v2.5.36 · Apr 2026 · source
TAXII push shipped Pushes MISP events to external TAXII collections on a schedule or on demand, with authentication and proxy support.
Also counts toward: Scheduled jobs
release 9 total
- Adds Bearer authentication support for TAXII servers, plus a streamlined add flow for basic auth. v2.5.43 · Jul 2026 · source · release history
- Adds Bearer authentication for TAXII servers and a streamlined add flow for basic auth; the TAXII API key field is renamed to Token and obfuscated in the server view. v2.5.43 · Jul 2026 · source · release history
- Adds proxy support for TAXII push operations. v2.5.42 · Jun 2026 · source · release history
- Adds scheduled TAXII push as a task type, supporting single-server and all-enabled push modes with a per-server enabled flag and blocking of pushes for disabled servers. v2.5.42 · Jun 2026 · source · release history
- Adds scheduled TAXII push as a new task type, with single-server and all-enabled push modes, a per-server enabled flag, and proxy support. v2.5.42 · Jun 2026 · source · release history
- TAXII 2 updated to spec and schema v148 conformance. v2.5.38 · May 2026 · source · release history
example
-
Enable scheduled TAXII push to all active servers so fresh MISP events are automatically pushed on a recurring schedule without manual intervention.
In the console, go to Server Settings & Maintenance > Scheduled Tasks, add a new task of type TAXII push, set push mode to all-enabled, and confirm the enabled flag is set to true for each target…v2.5.42 · Jun 2026 · source -
Enable and run a scheduled TAXII push to all enabled servers without waiting for the next cron window.
In the MISP UI, go to Server Settings > Scheduled Tasks, locate the TAXII push task, set the push mode to 'all-enabled', toggle the server's enabled flag on, then trigger the task manually.v2.5.42 · Jun 2026 · source -
Route TAXII push traffic through a corporate proxy so air-gapped or egress-controlled environments can still push threat intel to external TAXII collections.
In the console, go to Sync > TAXII Servers, open the target server's settings, and enter your proxy host and port in the Proxy fields before saving.v2.5.42 · Jun 2026 · source
Event templates shipped Lets users save a configured event layout as a reusable template so future events can be created consistently.
release 10 total
- Replaces the legacy template system with event templates, converting organisation-authored templates to active event templates. v2.5.50 · Oct 2026 · source · release history
- Save as template now operates via AJAX in the slide-in panel, keeping users on the current board. v2.5.39 · Jun 2026 · source · release history
- Save as template now saves via AJAX in the dashboard slide-in panel, keeping users on the current board. v2.5.39 · Jun 2026 · source · release history
-
All menu entry points to the legacy
/templates/*controller have been removed from the global menu, navbar helper, and side menus on both default and Overmind themes; the controller and view stack will be fully removed in 2.5.38. v2.5.37 · Apr 2026 · source · release history -
Introduces a completely redesigned Event Templating system with JSON-schema-backed templates (
event-template-v1), a drag-to-reorder builder UI, inline validation via/event_templates/validate_definition, and REST import/export with full object-template dependency tracking. v2.5.37 · Apr 2026 · source · release history -
New object templates Netflow and Network connection included with support for the
community-idfield. v2.4.111 · Jul 2019 · source · release history
ZeroMQ messaging integration verified Publishes MISP event data over a ZeroMQ message bus so downstream systems can consume it in real time.
release 7 total
- Adds zeromq supervisor setting and status check. v2.5.43 · Jul 2026 · source · release history
- Adds the Protected mode field in the event UI to attach PGP signing keys for cryptographic event synchronization v2.4.156 · Mar 2022 · source · release history
-
Adds
misp_json_warninglistto the ZMQ pub-sub channels for warning list updates v2.4.148 · Aug 2021 · source · release history - Warning list changes are exported in the ZMQ channel v2.4.145 · Jul 2021 · source · release history
-
Adds the
zmq_publishrole permission to enable or disable ZMQ publishing per user v2.4.92 · Jun 2018 · source · release history - Extends ZMQ feed protocol to support base64 encoded attachments v2.4.91 · May 2018 · source · release history
api
-
POST /sightings/add/{attributeId}· source · full API surface -
GET /sightings/index/{eventId}· source · full API surface -
POST /sightings/add· source · full API surface
Scheduled task management shipped Lets administrators create and monitor scheduled background tasks, with visibility into the server time and any upgrade errors.
Also counts toward: Command-line interface, Scheduled jobs
release 10 total
- Displays the current server time when scheduling a new scheduled task. v2.5.41 · Jun 2026 · source · release history
- Shows current server time when adding a scheduled task. v2.5.41 · Jun 2026 · source · release history
- Adds a supervisor-configuration scheduler during upgrade and surfaces upgrade errors directly to admins. v2.5.40 · Jun 2026 · source · release history
- Adds a periodic user summary scheduled task for generating regular reports. v2.5.18 · Aug 2025 · source · release history
-
Adds a new
last_run_atcolumn on tasks and improved job status handling in the task scheduler. v2.5.18 · Aug 2025 · source · release history -
New built-in Task Scheduler (site-admin only) lets administrators create and manage recurring actions for feeds, servers, workflows, and summaries — accessible at
/tasks— replacing external cron-based scheduling. v2.5.18 · Aug 2025 · source · release history
Additional attribute type support shipped suggested Adds support for x509-fingerprint-sha256, x509-fingerprint-md5, stix2-pattern, and whois-registrant-org attribute types.
Suggested capability: Threat indicator matching. This is our guess, not confirmed.
release 7 total
- Adds a dedicated UUID attribute type to satisfy FlowIntel and object template requirements, replacing ad-hoc text fields for unique identifiers. v2.5.26 · Nov 2025 · source · release history
-
Extends validation for
vulnerabilityattributes across all supported ID formats via vulnerability-lookup integration. v2.5.12 · May 2025 · source · release history - [data model] New attribute type weakness (CWS) added. v2.4.112 · Aug 2019 · source · release history
-
Adds
hassh-md5andhasshserver-md5as new attribute types for SSH implementation fingerprints v2.4.101 · Jan 2019 · source · release history -
Adds
cdhashandja3-fingerprint-md5as new standard attribute types for MISP events. v2.4.100 · Jan 2019 · source · release history -
Adds
x509-fingerprint-md5andx509-fingerprint-sha256attribute types to the network activity category v2.4.99 · Dec 2018 · source · release history
example
-
Add a new CWS (Common Weakness Scoring) attribute to an existing event.
# Create the event ID first if needed, then add attribute # Using PyMISP or API with new type curl -X POST "https://misp.local/events/addAttribute/12345" \ -H 'Authorization: YOUR_API_KEY' \ -d '{…v2.4.112 · Aug 2019 · source -
Create a new event with one of the new standard attribute types introduced in this release.
# Via MISP API or UI when adding attributes { "type": "cdhash", "value": "<code_signing_hash>" } { "type": "ja3-fingerprint-md5", "value": "<ssl_fingerprint>" }v2.4.100 · Jan 2019 · source -
Paginate through a large set of search results using the new parameters.
curl -k -H 'Authorization: YOUR_KEY' -H 'Accept: application/json' 'https://misp.example.com/restSearch/event?limit=100&page=2'v2.4.96 · Oct 2018 · source
Sharing group management shipped Exposes sharing groups as manageable entities via the API, enabling programmatic creation, management, and organization/server association.
Also counts toward: REST API
release 7 total
- Tightens access control logic for sharing group blueprints v2.4.216 · Nov 2025 · source · release history
- Adds the ability to define reusable sharing group blueprints using JSON filters (inheritance, metadata, boolean operators) to programmatically generate or update MISP sharing groups. v2.4.154 · Mar 2022 · source · release history
- Introduces filtering capabilities for sharing groups to locate specific events more accurately v2.4.136 · Jan 2021 · source · release history
-
Extends ACL to allow host org users to manage event blocklists via new
host_org_userpermission v2.4.131 · Sep 2020 · source · release history - The terms blacklist and whitelist are renamed to blocklist and includelist in the UI and API responses; scripts managing these must be updated. v2.4.131 · Sep 2020 · source · release history
- Updates sharing group management APIs with endpoints for adding/removing orgs and servers v2.4.88 · Feb 2018 · source · release history
example
-
Automate the creation of a sharing group that includes all Financial organizations and members of SG 127, while excluding those from Russia, Belarus, or their federations.
{ "AND": { "OR": { "org_sector": "Financial", "sharing_group_id": 127 }, "NOT": { "org_nationality": [ "Russia", "Russian Federation", "Belarus", "Republic of Belarus" ] } } }v2.4.154 · Mar 2022 · source -
Filter sharing groups to quickly find relevant events in large communities.
In the MISP interface, use the new filtering options on the sharing group list or event search to target information within specific sharing group repositories.v2.4.136 · Jan 2021 · source -
Use curl to add an organization to a sharing group via the new flexible API endpoints.
curl -X POST 'https://<misp>/sharingGroups/addOrg/<sg_id>/<org_id>/0' -H 'Authorization: <auth_key>'v2.4.88 · Feb 2018 · source
Extended attribute type support shipped suggested Adds support for new specific attribute types including Chrome extension IDs, Kusto queries, IDN domains, PGP keys, SHA3, and various file format identifiers.
Suggested capability: Threat indicator matching. This is our guess, not confirmed.
release 9 total
- Freetext extraction now supports Chrome and Edge browser extension IDs. v2.5.33 · Mar 2026 · source · release history
- Expands AttributeValidationTool to support more vulnerability ID types. v2.5.21 · Sep 2025 · source · release history
-
Adds new
dom-hashattribute type: a SHA-256-based structural fingerprint of an HTML page's DOM (tag names only, pipe-delimited, truncated to 32 chars) for sharing and correlating similar web pages such as phishing kits. v2.4.198 · Sep 2024 · source · release history - Adds Telegram bot object description type v2.4.165 · Nov 2022 · source · release history
-
Adds support for the
jarmindicator type in MISP and MISP standard format v2.4.135 · Dec 2020 · source · release history -
Adds
filename-pattern,cpe, andtelfhashattribute types for new data structures v2.4.133 · Oct 2020 · source · release history
Data export and privacy compliance shipped Provides capabilities for exporting user data for GDPR compliance and managing sensitive attribute deletion via dedicated UI buttons and API endpoints.
release
- New user login profiles feature enabling suspicious login detection and admin notifications. v2.4.180 · Dec 2023 · source · release history
-
Adds
last_password_changetimestamp field to user audit records. v2.4.176 · Sep 2023 · source · release history - Adds ability to recover deleted events from the diagnostics page using event history v2.4.133 · Oct 2020 · source · release history
-
Adds support for CPE associated object type
cpe-assetv2.4.133 · Oct 2020 · source · release history - Enables hard deleting of attributes that were never published to prevent leaking via soft deleted attributes v2.4.92 · Jun 2018 · source · release history
- Adds a new User Export button in the UI for GDPR data portability v2.4.90 · Apr 2018 · source · release history
example
-
View the login history for a user in the UI to leverage the new login profile capabilities.
Go to Users > View and select 'view_login_history' from the action menu for the target user.v2.4.180 · Dec 2023 · source -
Trigger a user data export for GDPR compliance via the new UI button.
In the Users menu, click the 'Export My Data' button to download your MISP information.v2.4.90 · Apr 2018 · source
XLSX export shipped Exports events, attributes, and sightings as Excel workbooks via restSearch and the per-event and mass export pickers, with a formula-safe escaping option that writes formula cells as literal apostrophe-prefixed strings to prevent formula injection.
Also counts toward: REST API
release
-
Adds XLSX export for events, attributes and sightings via
restSearchand the per-event and mass export pickers, withescape_formulas_literal:1parameter to use literal apostrophe escaping instead of thequotePrefixcell style.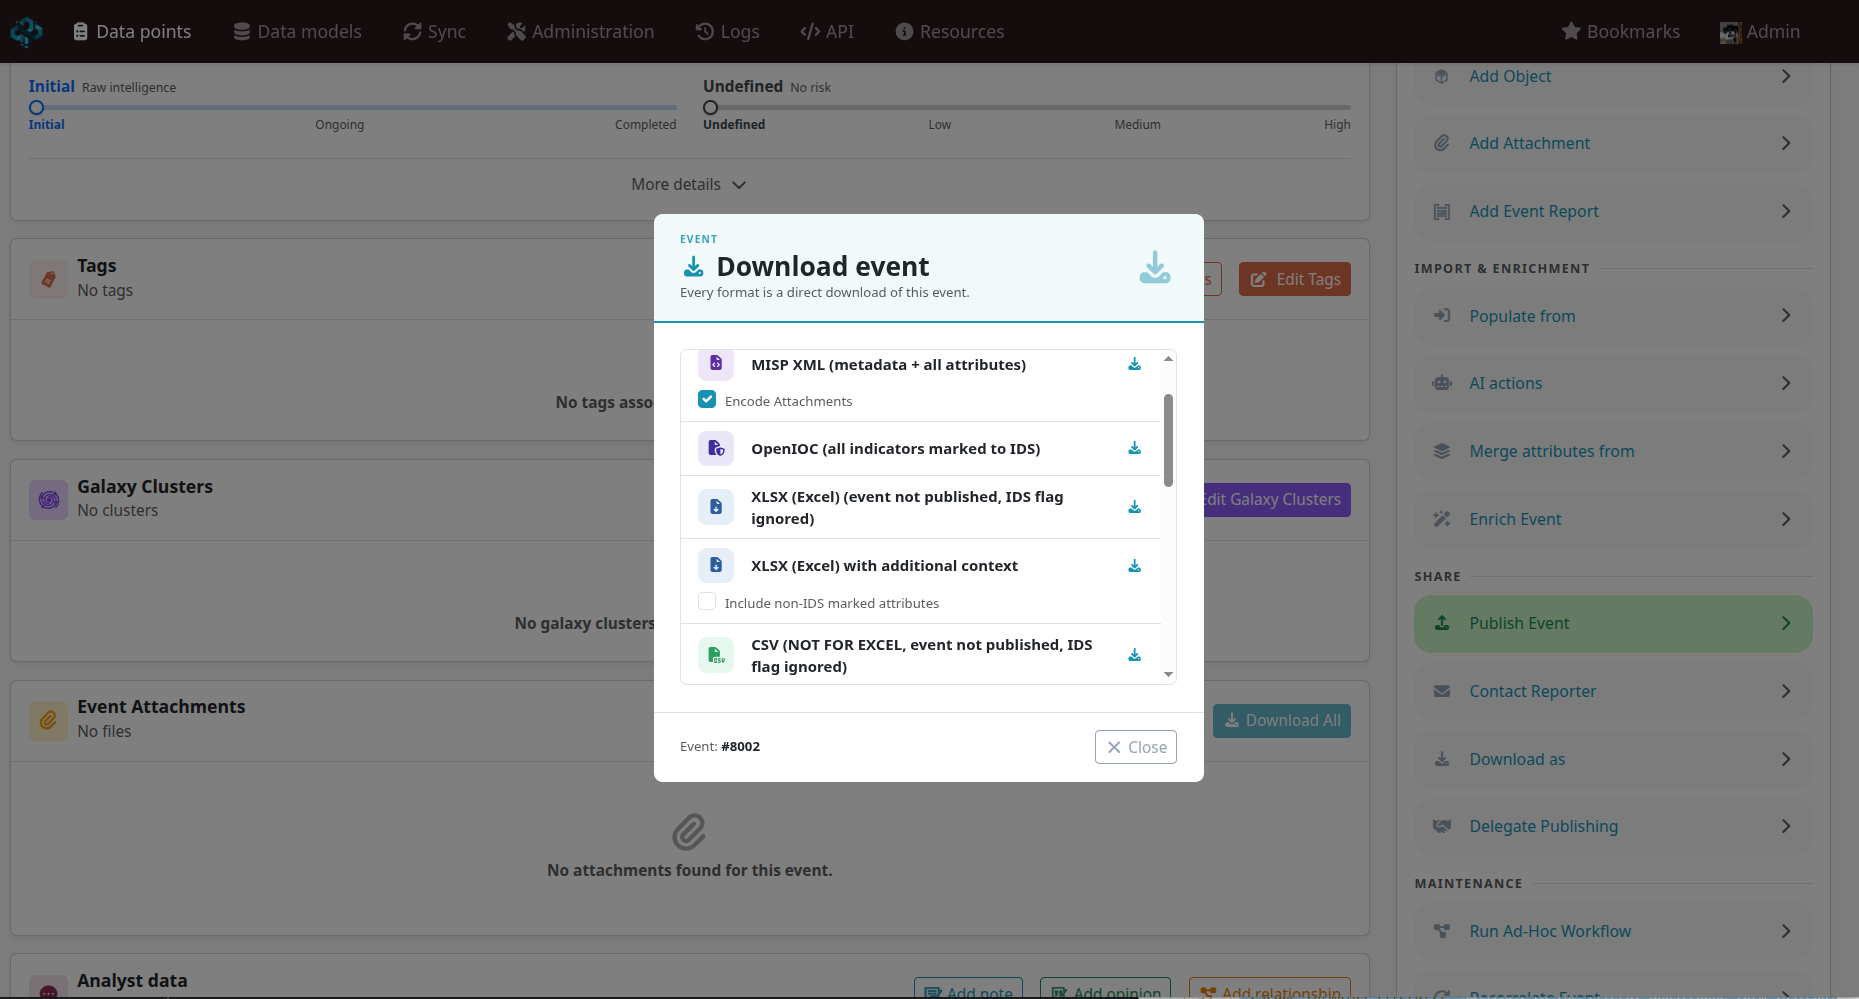 v2.5.48 · Sep 2026
· source
· release history
-
Adds XLSX export for events, attributes, and sightings via
restSearchand the per-event and mass export pickers, withescape_formulas_literal:1to switch formula-safe cells to literal apostrophe form instead ofquotePrefixcell style.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ v2.5.48 · Sep 2026 · source · release history -
Export endpoints unified into
restSearch, allowing direct downloads of search results in MISP-supported formats via the UI or API. v2.4.96 · Oct 2018 · source · release history -
limitandpageparameters now supported inrestSearchAPI calls for result pagination. v2.4.96 · Oct 2018 · source · release history
example
-
Export attributes as XLSX with formula cells written as literal apostrophe-prefixed strings, for workflows that re-export the workbook back to CSV without preserving
quotePrefixstyling.curl -s -H 'Authorization: <api-key>' -H 'Accept: application/vnd.openxmlformats-officedocument.spreadsheetml.sheet'…v2.5.48 · Sep 2026 · source -
Use literal apostrophe escaping when exporting to XLSX so that re-exporting the workbook back to CSV preserves values without the quotePrefix cell style.
curl -s -H 'Authorization: <api-key>' -H 'Accept: application/vnd.openxmlformats-officedocument.spreadsheetml.sheet'…v2.5.48 · Sep 2026 · source -
Export all attributes matching a network indicator search as an Excel workbook for analyst review — avoiding CSV formula-injection warnings in Excel.
curl -s -H 'Authorization: <api-key>' -H 'Accept: application/vnd.openxmlformats-officedocument.spreadsheetml.sheet' 'https://<misp-host>/attributes/restSearch/returnFormat:xlsx/type:ip-dst' -o…v2.5.48 · Sep 2026 · source
LLM-assisted analysis shipped Uses LLM integration for report summarisation and indicator extraction.
release
-
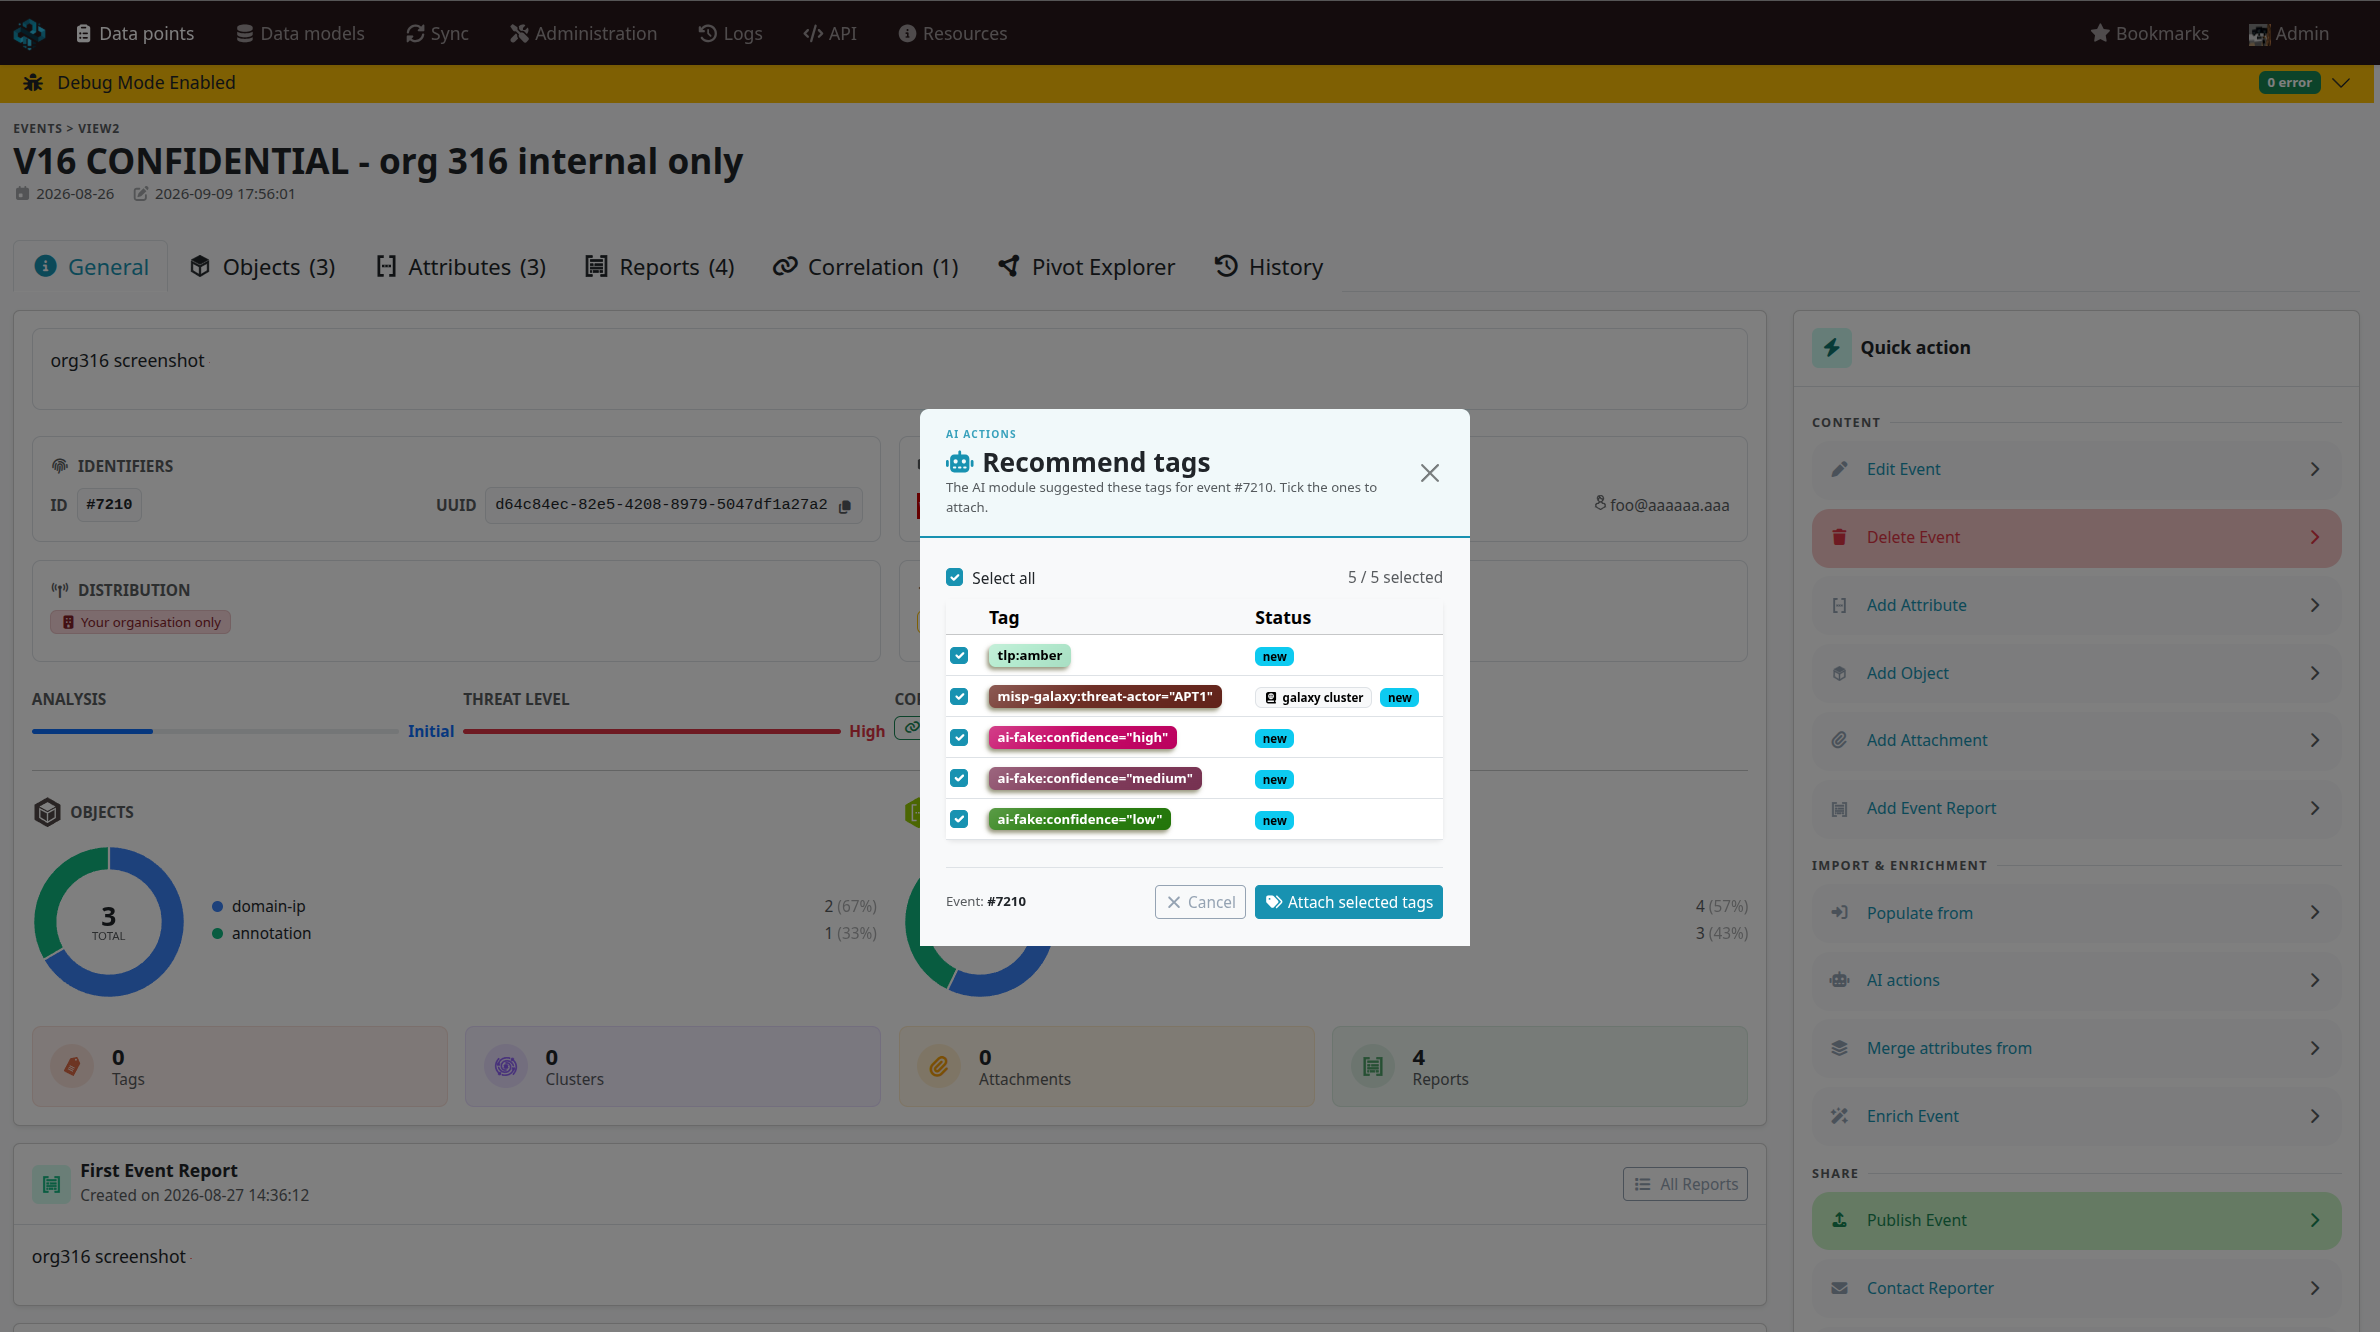
Adds AI-assisted event summarisation, tag recommendation, and indicator extraction via the
Plugin.AI_*server settings.
v2.5.47 · Sep 2026
· source
· release history
- Adds two workflow action modules: Summarise report with AI and Extract indicators with AI. v2.5.47 · Sep 2026 · source · release history
-
Adds
Plugin.AI_*settings under a new AI tab in server settings to configure the AI-assisted analysis integration, gated by the newperm_ai_toolsrole permission.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ v2.5.47 · Sep 2026 · source · release history -
Adds
docs/dev/ai_integration.mddocumenting the AI integration contract and actions, and includes a fake module server for testing without an LLM. v2.5.47 · Sep 2026 · source · release history -
Adds four AI-assisted analysis actions — summarise event, summarise report, recommend tags, and extract indicators — via the
ai_connectormisp-module; all AI-derived content is tagged withai-computer-assistedprovenance tags. v2.5.47 · Sep 2026 · source · release history - Adds initial LLM integration capabilities for report summarisation and extraction via stochasticCTIExtractor v2.4.179 · Nov 2023 · source · release history
example
-
Enable AI-assisted analysis for analysts by configuring the LLM endpoint and granting the required role permission via the AI tab in server settings.
In MISP, go to Administration > Server Settings & Maintenance > AI, set the `Plugin.AI_*` values for your LLM endpoint and model, then use the 'Test LLM' button to verify connectivity.v2.5.47 · Sep 2026 · source
Geolocation Map Visualisation shipped Renders geographic objects as interactive maps, tracks, and accuracy circles using custom tile servers.
release
- Updates geomap country sources in the dashboard to derive from geolocation and country-code objects. v2.5.43 · Jul 2026 · source · release history
- Adds accuracy-radius visualisation for geolocation objects, displayed as a toggleable circle on the map. v2.5.36 · Apr 2026 · source · release history
- Adds native GeoJSON rendering, enabling complex geographic shapes and features to be displayed on maps. v2.5.36 · Apr 2026 · source · release history
-
Adds configurable tile server support via
Plugin.Geolocation_url(defaults tohttps://geo.circl.lu). v2.5.36 · Apr 2026 · source · release history -
Adds interactive geolocation map rendering for objects with geographic coordinates directly in the event view, enabled via
Plugin.Geolocation_enabled. v2.5.36 · Apr 2026 · source · release history - Adds GPX track support so UAV and other GPS Exchange Format tracking data can be plotted as tracks on the map. v2.5.36 · Apr 2026 · source · release history
example
-
Enable geolocation map visualisation for events containing geographic objects, pointing to a self-hosted tile server.
app/Console/cake Admin setSetting Plugin.Geolocation_enabled true app/Console/cake Admin setSetting Plugin.Geolocation_url "https://tiles.example.com"v2.5.36 · Apr 2026 · source
MISP taxonomy enforcement shipped Enforces tag exclusivity rules within taxonomies to prevent conflicting tags in the user interface.
release
-
New
cloud-sovereigntyandai-computer-assistedtaxonomies added tomisp-taxonomies. v2.5.37 · Apr 2026 · source · release history -
Expands OpenAPI spec for
exportGalaxyClusters: documents additivedefault/custominclusion behavior and allowsdistributionto be passed as an array. v2.5.31 · Dec 2025 · source · release history - JSON schema updated to reflect latest MISP 2.5 features, enabling validation of new event structures. v2.5.27 · Nov 2025 · source · release history
- New option to prioritize UUID-based event linking over traditional IDs, improving consistency across distributed MISP instances. v2.5.26 · Nov 2025 · source · release history
- Adds a new setting to disable taxonomy checks when browsing data in the UI v2.4.159 · May 2022 · source · release history
- Enforces tag exclusivity rules within taxonomies in the MISP user-interface v2.4.118 · Nov 2019 · source · release history
example
-
Fetch galaxy clusters via the API passing
distributionas an array — now officially supported by the updated OpenAPI spec.curl -s -H 'Authorization: <your-api-key>' -H 'Accept: application/json' -H 'Content-Type: application/json' -X POST https://<misp-host>/galaxies/exportGalaxyClusters -d '{"default": true, "custom":…v2.5.31 · Dec 2025 · source
Warning list management shipped suggested Extends warning list capabilities to support dynamic updating by substring and toggling lists via API.
Suggested capability: Threat indicator matching. This is our guess, not confirmed.
Also counts toward: REST API
release 7 total
-
Warninglist filtering now supported on the
/attributes/searchendpoint. v2.5.13 · Jun 2025 · source · release history -
Warninglist filtering now supported in the
/attributes/searchendpoint. v2.4.211 · Jun 2025 · source · release history - Adds a new endpoint to let the instance sign arbitrary data on demand, gated by a new role permission and ACL setting. v2.4.201 · Dec 2024 · source · release history
- Adds a new endpoint to let the instance sign arbitrary data on demand, gated by a new role permission and ACL setting. v2.5.3 · Dec 2024 · source · release history
-
Adds
hhhash formatobject template for threat intelligence objects. v2.4.174 · Jul 2023 · source · release history - Warning lists can now be imported via the API v2.4.145 · Jul 2021 · source · release history
Correlation sensitivity configuration shipped suggested Allows administrators to configure fuzzy hashing match sensitivity via the `ssdeep_correlation_threshold` config key.
Suggested capability: Threat indicator matching. This is our guess, not confirmed.
release
-
Adds a
fast_updatemode to the/events/editendpoint to bypass duplicate validation for high-performance bulk updates v2.4.179 · Nov 2023 · source · release history -
orgc_idis added as a valid filter for the/events/restSearchAPI endpoint. v2.4.178 · Oct 2023 · source · release history - Enables adding values to a correlation exclusion list to prevent them from ever correlating again v2.4.142 · Apr 2021 · source · release history
- Provides a background task to retroactively execute exclusion rules on existing correlations v2.4.142 · Apr 2021 · source · release history
- Introduces a new tool to exclude specific values from the correlation engine to reduce noise v2.4.137 · Jan 2021 · source · release history
-
Adds
ssdeep_correlation_thresholdconfig key to control fuzzy hashing match sensitivity v2.4.88 · Feb 2018 · source · release history
example
-
Filter events in
/events/restSearchby organization ID using the neworgc_idparameter.curl -X GET "https://misp.example.org/events/restSearch?orgc_id=12345" -H "Authorization: <key>"v2.4.178 · Oct 2023 · source
Advanced tag filtering shipped Supports positive and negative tag lookups, blocked attribute filtering, and inclusion of object-level details in exports.
release
-
Signature allowedlist filtering no longer unconditionally removes matching values from
restSearch, TAXII push, OpenIOC, and Bro exports — exclusion now applies only whenenforceWarninglistis enabled. v2.5.50 · Oct 2026 · source · release history - Searches now use POST requests backed by a Redis token-based system, enabling flawless pagination on complex queries and independent concurrent search tabs. v2.5.13 · Jun 2025 · source · release history
- Attribute and log searches now use POST requests backed by a Redis token system, enabling pagination on complex queries and multiple independent search tabs simultaneously. v2.4.211 · Jun 2025 · source · release history
- Introduces a pluggable warning system that warns users about event quality improvements such as tagging issues v2.4.156 · Mar 2022 · source · release history
- Adds a new related tags feature to display the most commonly used tags for a specific attribute across all events. v2.4.97 · Oct 2018 · source · release history
- Enhances tag filtering to support positive lookup on events/attributes, negative lookup on events, and blocked attribute filtering within matched events v2.4.83 · Dec 2017 · source · release history
Probabilistic data structure object support shipped Adds a new MISP object template for probabilistic data structures to enrich threat intelligence events.
release
-
Adds
UrlEgressValidatorclass to validate outbound URL schemes and block loopback or private destinations
v2.5.46 · Sep 2026
· source
· release history
-
Extends
CurlClientwith host pinning, controlled redirects, response size limits, and default TLS peer verification v2.5.46 · Sep 2026 · source · release history -
Introduces a shared
UrlEgressValidatorthat enforces a common outbound URL policy — validating schemes and resolved addresses and blocking loopback, link-local, and private destinations across all remote-resource retrieval paths.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ v2.5.46 · Sep 2026 · source · release history -
Extends
CurlClientwith host pinning, controlled and validated redirects, response size limits, and TLS peer verification enabled by default. v2.5.46 · Sep 2026 · source · release history -
sessionkill-switch API endpoint added to terminate active sessions for integration with MeliCERTes project v2.4.167 · Dec 2022 · source · release history - Probabilistic data structure object added as a new template. v2.4.153 · Feb 2022 · source · release history
API rate limiting and throttling shipped Implements per-role request throttling for restSearch endpoints with header-based quota notifications.
Also counts toward: REST API
release
-
Enforces
distribution=0filter in REST searchfetchEvent.
v2.5.45 · Aug 2026
· source
· release history
-
Adds on-demand recorrelation of any event for site admins, accessible through the UI or via the API endpoint
/events/recorrelate/{event_id}. v2.5.21 · Sep 2025 · source · release history - Adds support for *top correlations* in the on-demand correlation engine, enabling ranked correlation views on demand. v2.5.19 · Aug 2025 · source · release history
- New OnDemand Correlation Engine fetches correlating values live without persistent storage, reducing disk usage and eliminating the need to re-run correlation jobs. v2.5.18 · Aug 2025 · source · release history
-
Adds per-role
restSearchthrottling (rate limits on heavy search queries within a 15-minute window) with header-based quota notifications for API users v2.4.117 · Oct 2019 · source · release history
example
-
Cap how many results a high-volume analyst role can pull per API call to protect server resources.
In the console, go to Administration > List Roles, edit the target role, and set the maximum API result limit field to the desired value (e.g. 10000).v2.4.213 · Jun 2025 · source
Proxy configuration for outbound connections verified Routes outbound HTTP traffic, including TAXII connections, through a configured proxy server.
Also counts toward: Command-line interface
release
- New OIDC auth setting to skip or enforce global MISP proxy settings. v2.5.32 · Jan 2026 · source · release history
command line
-
--proxy_method — HTTP proxy authentication method configured in MISP.v2.5.42 · Jun 2026 · command-line history -
--proxy_host — HTTP proxy host to use for TAXII requests.v2.5.42 · Jun 2026 · command-line history -
--proxy_password — HTTP proxy authentication password.v2.5.42 · Jun 2026 · command-line history -
--proxy_port — HTTP proxy port to use for TAXII requests.v2.5.42 · Jun 2026 · command-line history -
--proxy_user — HTTP proxy authentication username.v2.5.42 · Jun 2026 · command-line history
ATT&CK heatmap shipped Shows which ATT&CK techniques and sub-techniques are covered by current intelligence, using colour intensity to indicate volume.
release
- ATT&CK heatmap redesigned with parent/sub-technique aggregation, inactive technique hiding, readable labels, and a clearer red intensity ramp. v2.5.39 · Jun 2026 · source · release history
- Redesigned ATT&CK heatmap with parent/sub-technique aggregation, inactive technique hiding, readable labels, and a clearer red intensity ramp. v2.5.39 · Jun 2026 · source · release history
- Adds GPX track support so UAV and other GPS Exchange Format tracking data can be plotted as tracks on the map. v2.5.36 · Apr 2026 · source · release history
- Updates MITRE ATT&CK framework support to version 12.0 v2.4.165 · Nov 2022 · source · release history
-
Adds
TagCollectioncapability to predefine reusable structures of tags (from taxonomies) and galaxy information for quick classification v2.4.101 · Jan 2019 · source · release history
example
-
Search attributes while suppressing hits that match warning-list entries, reducing noise in bulk hunts.
curl -s -X POST -H 'Authorization: <your-api-key>' -H 'Content-Type: application/json' -H 'Accept: application/json' -d '{"value": "<ioc-value>", "warninglist": 1}'…v2.5.13 · Jun 2025 · source
Correlation noise reduction shipped Allows administrators to exclude specific values from correlation calculations and retroactively apply these exclusions to reduce false-positive matches.
release
- Bi-directional correlation rule exclusions: existing data now avoids correlating against newly added data when exclusion rules apply, ensuring consistent suppression in both directions. v2.5.15 · Jun 2025 · source · release history
- Bi-directional correlation rule exclusions: existing data now correctly avoids correlating against newly added information when exclusion rules apply, not just the reverse. v2.4.213 · Jun 2025 · source · release history
- New correlation rule system lets site admins define de-correlation rules — by org_id, orgc_id, event_id, or event_info (with substring matching) — to suppress noisy cross-correlations between selected events while still allowing those events to correlate with non-matching events. v2.4.195 · Aug 2024 · source · release history
- Provides a background task to retroactively execute exclusion rules on existing correlations v2.4.142 · Apr 2021 · source · release history
- Introduces a new tool to exclude specific values from the correlation engine to reduce noise v2.4.137 · Jan 2021 · source · release history
example
-
Exclude recurring daily scan events from correlating with each other using event title substring matching.
{ "selector_type": "event_info", "selector_list": [ "%] Daily scan results", "Weekly scan results week #%" ] }v2.4.195 · Aug 2024 · source
Training topology deployment shipped Provides a deployment script for setting up networked MISP instances specifically for training purposes.
release
- Supports Docker-based installation and upgrade to MISP 2.5 via the updated MISP-docker project. v2.5.0 · Oct 2024 · source · release history
- Replaces legacy dependencies with modern PHP 8.x-compatible alternatives across the core platform. v2.5.0 · Oct 2024 · source · release history
-
Introduces new native installation and upgrade scripts targeting Ubuntu 24.04 (
INSTALL.ubuntu2404.shandUPGRADE.ubuntu2404.sh). v2.5.0 · Oct 2024 · source · release history - Adds PHP 8.1+ support via an updated CakePHP fork, enabling MISP to run on a modern, non-EOL PHP runtime. v2.5.0 · Oct 2024 · source · release history
-
Adds
Security.alert_on_suspicious_loginsconfiguration key for security audit alerts v2.4.183 · Jan 2024 · source · release history -
Adds
TrainingShelldeployment script for networked MISP training topologies v2.4.106 · Apr 2019 · source · release history
Flexible event attribute filtering shipped Provides a tool at the event level that supports complex rules for filtering large sets of attributes.
release
-
Migrates legacy signature allowedlists into an enabled custom regular-expression warninglist covering all attribute types; filtering now applies only when
enforceWarninglistis enabled. v2.5.50 · Oct 2026 · source · release history -
Optimizes tag filtering logic by dynamically choosing between
EXISTSandUNIONquery strategies based on attribute filter weight. v2.5.28 · Dec 2025 · source · release history -
Filter attributes by
object_relationfield in search queries, adding a new dimension to attribute lookups. v2.5.15 · Jun 2025 · source · release history - New checkbox in the event view for selecting object attributes directly. v2.4.203 · Jan 2025 · source · release history
- Adds a new flexible attribute filtering tool at the event level that supports complex rules for large events. v2.4.103 · Mar 2019 · source · release history
LDAP role and organization mapping shipped Maps MISP users to organizations and roles based on LDAP group membership or directory fields using configurable settings.
release
-
Adds
ldapOrgGroupMappingandldapRoleGroupMappingsettings whose precedence follows settings order, supporting role and organisation mapping via directory field or group membership.
v2.5.45 · Aug 2026
· source
· release history
- Adds LDAP support for role and organisation mapping via directory fields or group membership v2.5.45 · Aug 2026 · source · release history
-
Adds
ldapNestedGroupssetting to resolve nested LDAP group membership for role and org mapping. v2.5.45 · Aug 2026 · source · release history -
Adds
ldapNestedGroupssetting to resolve nested group membership in LDAP auth v2.5.45 · Aug 2026 · source · release history -
LDAP plugin gains support for
memberOfqueries. v2.5.37 · Apr 2026 · source · release history
Admin security diagnostics shipped Alerts administrators to insecure instance-level security settings so they can be resolved before causing exposure.
release
-
Warns admins when the
check_sec_fetch_site_headersetting is unset, flagging elevated risk on multi-homed/multi-tenant instances. v2.5.40 · Jun 2026 · source · release history - Adds Security Audit tool in server settings diagnostics section to check security posture and CSP configuration v2.4.140 · Mar 2021 · source · release history
example
-
Check whether your instance is flagging the dangerous default — navigate to the admin diagnostics page to see the new warning about check_sec_fetch_site_header.
In the MISP admin console, go to Administration > Server Settings & Maintenance > Diagnostics and look for the new warning banner about check_sec_fetch_site_header being unset.v2.5.40 · Jun 2026 · source -
Look up all IPs associated with a specific user account for auditing.
MISP/app/Console/cake Admin UserIP <user_id>v2.4.122 · Feb 2020 · source -
Identify which user account is associated with a specific IP address.
MISP/app/Console/cake Admin IPUser <ip>v2.4.122 · Feb 2020 · source
Sighting policy enforcement shipped Provides mechanisms to enforce sighting policies, including blocklist filtering for specific organizations and toggling API-driven loading.
Also counts toward: REST API
release
- Changes default sighting visibility to Everyone (previously Event Owner). v2.5.31 · Dec 2025 · source · release history
- Adds a sighting blocklist subsystem to filter organisations from sighting sync negotiations in Sightings > Blocklist v2.4.189 · Apr 2024 · source · release history
-
Introduces sighting policy enforcement in the
sightings:getLastSightingfunction v2.4.188 · Mar 2024 · source · release history -
Adds
MISP.sightings.enabledconfig key to toggle API-driven sighting data loading forrestsearchand/events/viewendpoints v2.4.188 · Mar 2024 · source · release history -
Adds
Sightings_anonymise_assetting to anonymise pushed sightings. v2.4.132 · Sep 2020 · source · release history
Global sightings management shipped Enables the creation and handling of global-level sightings in addition to existing per-attribute sightings via REST API and UI.
Also counts toward: REST API
release
-
New event index and REST API filtering by whether an event is
extendingorextendedby another event. v2.5.13 · Jun 2025 · source · release history -
event_timestamp,attribute_timestamp, andpublish_timestamptimestamp filters added to/attributes/restSearchfor precise time-based querying. v2.4.119 · Dec 2019 · source · release history -
attributes/restSearchnow acceptsincludeSightingsandincludeCorrelationsparameters to add context to results. v2.4.112 · Aug 2019 · source · release history -
attributes/restSearchJSON output now includes additional event fields when usingIncludeContext. v2.4.112 · Aug 2019 · source · release history - Enables global-level sightings in addition to per-attribute sightings via the REST API and UI v2.4.102 · Feb 2019 · source · release history
Analyst relationship mapping shipped Allows analysts to explicitly define and store custom structural relationships between cyber tool elements beyond default attribute linking.
release
-
Adds CRUD and highlighting support for
relationship_typesin object relationships. v2.5.8 · Mar 2025 · source · release history -
Adds support for the
highlightedfield in object-relationship/addand/editendpoints. v2.5.8 · Mar 2025 · source · release history -
Object relationship
/addand/editendpoints now support thehighlightedfield. v2.4.206 · Mar 2025 · source · release history -
Adds CRUD and visual highlighting support for
relationship_typesin object relationships. v2.4.206 · Mar 2025 · source · release history - Adds the ability to define Analyst Relationships between elements in MISP v2.4.186 · Mar 2024 · source · release history
JSON event population workflow shipped Allows populating new events with attributes and objects by uploading or pasting JSON files containing MISP event content.
release
- Supports uploading protected events via the import MISP JSON functionality. v2.4.201 · Dec 2024 · source · release history
- Supports uploading protected events via the import MISP JSON functionality. v2.5.3 · Dec 2024 · source · release history
- Adds textarea input for uploading MISP events via pasted data alongside existing file upload v2.4.159 · May 2022 · source · release history
- Adds a new event population workflow: uploading a JSON file containing MISP elements via the UI option "Populate from... > Populate using a JSON file containing MISP event content data". v2.4.154 · Mar 2022 · source · release history
example
-
Pre-populate an existing event with attributes and objects from a local JSON file via the UI instead of manual entry.
In the Event editor, click 'Populate from...' > 'Populate using a JSON file containing MISP event content data' > Upload your JSON file.v2.4.154 · Mar 2022 · source
Database migration management shipped Provides CLI commands and a ledger-based system for previewing, applying, and creating database schema migrations.
Also counts toward: Command-line interface
release
-
Introduces migration management CLI commands:
cake Admin migrationStatus,cake Admin migrationApply(with--dry-run), andcake Admin migrationCreate.
v2.5.47 · Sep 2026
· source
· release history
-
Adds
cake Admin migrationStatus,cake Admin migrationApply(with--dry-runto preview SQL), andcake Admin migrationCreateconsole commands for the new ledger-based migration system. v2.5.47 · Sep 2026 · source · release history
Schema consistency checks shipped Validates database schema model consistency for upcoming upgrade paths and highlights divergences.
release
-
Fleet monitoring queries for
actual_db_versionvsexpected_db_versionwill stop working; these must be replaced withmigrations_pendingandmigrations_failedfields in the diagnostic payload.
v2.5.47 · Sep 2026
· source
· release history
-
Migrates database schema management from a single
db_versioninteger to aschema_migrationsledger underapp/Lib/Migration/Migrations/, with pending and failed migrations now exposed asmigrations_pendingandmigrations_failedfields in the diagnostic payload. v2.5.47 · Sep 2026 · source · release history - Adds database schema model consistency checks for upcoming upgrade paths v2.4.118 · Nov 2019 · source · release history
example
-
Check which database migrations are pending or failed before or after an upgrade, to verify schema state across a fleet.
cake Admin migrationStatusv2.5.47 · Sep 2026 · source
Dynamic authentication plugin loading shipped Allows the system to load specific authentication plugins dynamically via configuration, reducing manual bootstrap requirements and improving flexibility.
Also counts toward: Plugin system
release
-
Adds authentication against a header asserted by a trusted proxy
v2.5.45 · Aug 2026
· source
· release history
- Adds authentication against a header asserted by a trusted proxy as an LDAP auth option. v2.5.45 · Aug 2026 · source · release history
- Introduces support for loading authentication plugins dynamically based on configuration settings. v2.5.10 · May 2025 · source · release history
-
Introduces support for loading authentication plugins (e.g.,
OidcAuth) based on configuration settings rather than requiring manual bootstrap code. v2.4.208 · May 2025 · source · release history
Freetext attribute import verified Lets analysts paste unstructured text and have it automatically parsed into typed MISP attributes.
release
- Adds support for EM SPACE (U+2003) in FreeText import, broadening freetext attribute parsing. v2.5.39 · Jun 2026 · source · release history
- Supports EM SPACE (U+2003) in FreeText import for broader indicator parsing coverage. v2.5.39 · Jun 2026 · source · release history
- New Import Choice button surfaced above the attribute list directly on the event view page. v2.5.15 · Jun 2025 · source · release history
api
-
GET /attributes/describeTypes· source · full API surface
MISP community discovery shipped Provides tools and pages for browsing known MISP communities and generating public discovery webpages.
Also counts toward: Command-line interface
release
- Adds CSIRT.SK to the Slovak MISP Community defaults and meta community vetting process. v2.5.28 · Dec 2025 · source · release history
- Adds Threatmon MISP Community to the community list. v2.4.202 · Dec 2024 · source · release history
- Adds a new command-line tool to generate the communities webpage, helping users find the right MISP communities. v2.4.126 · Jun 2020 · source · release history
example
-
Generate the HTML page listing all MISP communities for public discovery.
python /opt/misp/PyMISP/scripts/generate_community_page.pyv2.4.126 · Jun 2020 · source
Signed data endpoint shipped Exposes a new API endpoint allowing the instance to sign arbitrary data on demand, controlled by role permissions and ACL settings.
Also counts toward: Role-based access control
release
-
New
flowintel-create-caseworkflow module enables automated case creation in flowintel directly from MISP workflows. v2.5.27 · Nov 2025 · source · release history - Adds a new endpoint to let the instance sign arbitrary data on demand, gated by a new role permission and ACL setting. v2.4.201 · Dec 2024 · source · release history
- Adds a new endpoint to let the instance sign arbitrary data on demand, gated by a new role permission and ACL setting. v2.5.3 · Dec 2024 · source · release history
example
-
Automatically open a flowintel case when a MISP event meets a trigger condition — wire the new module into an existing workflow.
In the MISP console, go to Event Actions > Workflows, open or create a workflow, search for the module `flowintel-create-case` in the module palette, drag it onto the canvas, configure the flowintel…v2.5.27 · Nov 2025 · source
Database diagnostics and optimization shipped Provides tools to track database table sizes, check optimization potential, and compare the current DB state against a reference schema.
release
-
Extends the
/benchmarks/sqlMetricsendpoint with/explainand/analyzepath parameters to run SQL EXPLAIN or ANALYZE on slow queries. v2.5.23 · Oct 2025 · source · release history - New database diagnostics subsystem compares current DB state against reference schema, highlighting divergences and generating corrective SQL queries. v2.4.119 · Dec 2019 · source · release history
- Adds a new diagnostic tool for administrators to track database table sizes and potentially recoverable space via optimization v2.4.114 · Aug 2019 · source · release history
example
-
Check database optimization potential via the admin dashboard
Access the new diagnostic tool in the administrator settings to view table sizes and recoverable space metrics.v2.4.114 · Aug 2019 · source
Comprehensive audit logging shipped Enables full audit logging via ZeroMQ or Syslog with severity levels for all entries.
release
- Generates error logs in NDJSON format for easier parsing and integration with modern logging systems v2.4.214 · Jul 2025 · source · release history
- Error log entries now include the user that caused the exception and the exact codebase location where it occurred. v2.5.16 · Jul 2025 · source · release history
- Adds creation timestamps to application logs for improved event tracking and chronological analysis. v2.4.204 · Jan 2025 · source · release history
- Enables full audit logging via ZMQ or Syslog with proper severity levels for all audit log entries v2.4.83 · Dec 2017 · source · release history
Organisation email domain restrictions shipped Allows restricting user login to specific email domains at the organisation level.
release
-
The
extend[ing/ed]parameter for merging data has been renamed to theinclude_*syntax; existing API calls usingextendingorextendedfor merge operations must be updated. v2.5.13 · Jun 2025 · source · release history -
The
extend[ing/ed]parameter for merging data has been renamed toinclude_*syntax; existing API calls usingextendingorextendedfor merging must be updated. v2.4.211 · Jun 2025 · source · release history - Adds new setting to block event publication if the publishing user is the creator of the event v2.4.184 · Feb 2024 · source · release history
-
Adds
email_domain_restrictionsconfiguration at the organisation level to limit which email domains users within that organisation can use for login v2.4.83 · Dec 2017 · source · release history
MISP community federation shipped Allows browsing known MISP communities, sending access requests, and searching for pending delegation requests via the UI.
release
- Adds the Threatmon MISP Community to the platform's community integrations. v2.5.6 · Jan 2025 · source · release history
- Adds a new communities view under sync actions for browsing known MISP communities and sending access requests directly to administrators v2.4.114 · Aug 2019 · source · release history
example
-
Browse known communities and send an access request from within the web UI
In the navigation menu, go to sync actions -> communities, then select a community and click 'Request Access'.v2.4.114 · Aug 2019 · source -
Search for pending delegation requests without using the API or shell
In the navigation menu, go to the delegation request search interface and filter by 'received' or 'issued'.v2.4.114 · Aug 2019 · source
Periodic summary notifications shipped Sends daily, weekly, or monthly data snapshots and trend charts via email or UI to subscribed users.
release
- Adds a configurable number-of-days field in the UI for user periodic reporting. v2.4.175 · Aug 2023 · source · release history
- Periodic notification charts now only show data for tags that have changed over time. v2.4.163 · Sep 2022 · source · release history
- New correlations are now displayed in the periodic notification summary. v2.4.163 · Sep 2022 · source · release history
- Adds periodic summary feature for daily, weekly, and monthly data snapshots, sent via email or UI to subscribed users. v2.4.162 · Sep 2022 · source · release history
Event summary notifications shipped Enables sending email alerts containing only event metadata and summaries, excluding the full attribute and object payloads.
release
- Email notifications include a new configuration setting for event summaries only, excluding attributes and objects v2.4.145 · Jul 2021 · source · release history
- Warning lists can now be imported via the API v2.4.145 · Jul 2021 · source · release history
- Adds backend support for sending HTML formatted email notifications v2.4.141 · Apr 2021 · source · release history
-
Adds
MISP.event_alert_metadata_onlyconfiguration key to control email alert payload contents v2.4.141 · Apr 2021 · source · release history
Analyst opinion and note tagging shipped Allows users to add qualitative ratings and free-text notes to any MISP element, including events, objects, and attributes.
release
- Migrates legacy event discussions (Thread/Post) to analyst notes, preserving author organisation, timestamps, and visibility information. v2.5.50 · Oct 2026 · source · release history
- The legacy Thread/Post discussion workflow trigger is removed; workflows that relied on it are logged during migration and will no longer fire. v2.5.50 · Oct 2026 · source · release history
- Adds the ability to add an Analyst Opinion with a rating (0-100) to any MISP element v2.4.186 · Mar 2024 · source · release history
Event report PDF export shipped Allows exporting finalized event reports as formatted PDF files using Pandoc for stakeholder distribution.
release
- Adds PDF downloads from event report quick actions in Overmind. v2.5.50 · Oct 2026 · source · release history
example
-
Export a finished Event Report as a properly formatted PDF for sharing outside MISP.
Open the Event Report, click the Download menu, and select 'Download as PDF' (requires the `convert_markdown_to_pdf.py` misp-module and its dependencies: Pandoc, wkhtmltopdf, mermaid-cli).v2.5.2 · Nov 2024 · source -
Export a finished Event Report as a polished PDF for stakeholder distribution, using Pandoc rather than the browser print dialog.
Open the Event Report, click the download icon and select 'Download as PDF' — requires `convert_markdown_to_pdf.py` from misp-modules and Pandoc, wkhtmltopdf, and mermaid-cli installed on the MISP…v2.4.200 · Nov 2024 · source
Attribute enrichment endpoint shipped Provides a direct REST endpoint to execute enrichment modules on specific attributes without requiring full event processing.
Also counts toward: REST API
release
-
Enforces Event modify ACL on attribute enrichment requests.
v2.5.45 · Aug 2026
· source
· release history
-
GET/POST /attributes/enrich/[attribute_id|attribute_uuid]endpoint added to execute enrichment modules on specific attributes. v2.4.193 · Jun 2024 · source · release history
example
-
Run enrichment modules on a specific attribute via API.
curl -X POST https://misp.local/attributes/enrich/[attribute_id] \ -H 'Authorization: YOUR_AUTH_KEY' \ -d '{"dns": 1}'v2.4.193 · Jun 2024 · source
CSV object detail export shipped Includes object-level details such as UUID and name in CSV exports via query parameters.
Also counts toward: CSV data export
release
-
Adds
object_attributesquery parameter to MISP CSV export to include object-level columns v2.4.82 · Nov 2017 · source · release history
example
-
Enable debug mode in MISP and use the new Overmind theme visual section to inspect debug output directly in the UI.
In the MISP console, go to Administration > Server Settings & Maintenance, enable Debug mode, then switch your theme to Overmind to see the new visual debug section.v2.5.34 · Mar 2026 · source -
Include object-level details like UUID and name in CSV export
GET https://<misp-instance>/events/csv/download/<event-id>?attributes=timestamp,type,uuid,value&object_attributes=uuid,namev2.4.82 · Nov 2017 · source
REST client history and bookmarks shipped Maintains a history of recent queries in the REST client with the ability to bookmark frequently used ones.
release
-
The
urlfield in Bookmarks has been renamed totext; any integration or script referencing theurlfield by name will break. v2.5.29 · Dec 2025 · source · release history -
Bookmark creation now supports sharing with all users in the same organization via the
exposed_to_orgfield v2.4.194 · Jun 2024 · source · release history - REST client history of the 10 most recent queries with bookmark capability v2.4.104 · Mar 2019 · source · release history
Role-based API throttling shipped Enables administrators to set maximum result limits per API request at the role level to control resource usage during bulk operations.
release
- Role-based API result limits: administrators can configure a maximum number of results returned per API request at the role level for granular resource control. v2.5.15 · Jun 2025 · source · release history
- Role-based API result limits: administrators can now configure a maximum number of results returned per API request at the role level for granular resource control. v2.4.213 · Jun 2025 · source · release history
example
-
Set a per-role API result cap to prevent high-volume users from overwhelming the instance during bulk exports.
In the Admin console, go to Administration > Roles, edit the target role, and set the maximum number of results per API request in the role configuration.v2.5.15 · Jun 2025 · source
Kunai export format shipped Enables exporting MISP events in Kunai format via the search API to feed Linux host-based monitoring pipelines.
Also counts toward: REST API
release
- New Kunai export format available via restSearch, enabling Linux endpoint monitoring data export from MISP events. v2.5.1 · Oct 2024 · source · release history
example
-
Export MISP events in Kunai format via restSearch to feed into Linux host-based monitoring with Kunai.
curl -H 'Authorization: <your-api-key>' -H 'Accept: application/json' -H 'Content-Type: application/json' -X POST https://<misp-instance>/events/restSearch -d '{"returnFormat": "kunai", "tags":…v2.5.1 · Oct 2024 · source -
Export MISP events in Kunai format via restSearch to feed into Linux endpoint monitoring pipelines.
curl -H 'Authorization: <your-api-key>' -H 'Accept: application/json' 'https://<misp-instance>/events/restSearch/returnFormat:kunai'v2.4.199 · Oct 2024 · source
Email notification workflow module shipped suggested Adds an email-specific module to workflows that supports recipient lists and Jinja templating.
Suggested capability: Response playbook automation. This is our guess, not confirmed.
release
-
Allows org admins and all admins to use the
workflow-module:send_mailmodule to receive send_log_mail events. v2.4.170 · Apr 2023 · source · release history -
The
workflowsmodule now requires misp-modules for email functionality. v2.4.170 · Apr 2023 · source · release history -
Adds
emailnotification module in workflows supporting list recipients and Jinja templating. v2.4.162 · Sep 2022 · source · release history
ATT&CK matrix export shipped Returns ATT&CK matrix data in HTML format for analysis via the search API.
Also counts toward: REST API
release
- Adds an HTML export format for filtering data and generating a summary with Mitre ATT&CK matrix and context labels v2.4.156 · Mar 2022 · source · release history
-
Extends
restSearchto support searching by creator organisation (orgc.*fields) and meta fields in galaxy clusters (galaxy.*) v2.4.118 · Nov 2019 · source · release history -
New
attackexport format forrestSearchAPI returning ATT&CK matrix data as HTML v2.4.107 · May 2019 · source · release history
Attribute distribution visualization shipped Provides UI components to visualize and verify the sharing levels and distribution of attributes within an event.
release
- New distribution visualisation graph showing potential recipients of events and attributes v2.4.104 · Mar 2019 · source · release history
- Adds distribution and sharing visualisation UI to verify attribute sharing levels within an event v2.4.91 · May 2018 · source · release history
example
-
Visualise where shared data will go using the distribution graph.
Open the distribution visualisation graph in the event/attribute viewv2.4.104 · Mar 2019 · source
CSV export column selection shipped Allows selecting specific event and attribute columns during CSV download via URL parameters.
Also counts toward: CSV data export
release
- Adds CSV export option to the Event index API alongside existing JSON format. v2.4.97 · Oct 2018 · source · release history
-
Adds
GET /events/csv/download/<event-id>?attributes=...parameter to select specific CSV export columns v2.4.82 · Nov 2017 · source · release history
example
-
Export specific event columns to CSV for targeted analysis
GET https://<misp-instance>/events/csv/download/<event-id>?attributes=timestamp,type,uuid,valuev2.4.82 · Nov 2017 · source
Programmatic role administration shipped Provides administrators with command-line tools to programmatically manage user roles, permissions, and access boundaries outside the web UI.
Also counts toward: Command-line interface, Role-based access control
release
-
Adds
objectRelationUsagestatistics operation reporting how frequently relations are populated across MISP objects, grouped by the latest version of each object template.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ v2.5.50 · Oct 2026 · source · release history - Adds new role management command accessible via the MISP shell interface v2.4.187 · Mar 2024 · source · release history
Module tag removal shipped Allows enrichment and import modules to include a remove_tags list in their result rows so that existing tags can be stripped from target attributes, with removed tags surfaced in the resolution screen and enrichment output.
release
-
Adds
remove_tagslist support in enrichment and import module result rows, letting modules strip tags from existing attributes instead of creating duplicates, with removed tags surfaced in the resolution screen andEventShellenrichment output.
v2.5.48 · Sep 2026
· source
· release history
-
Adds
remove_tagslist support in misp-module result rows, allowing enrichment and import modules to strip tags from the target attribute, with removed tags reported in the resolution screen andEventShellenrichment output. v2.5.48 · Sep 2026 · source · release history
LDAP account synchronization and mapping shipped Synchronizes user accounts from LDAP, including disabling accounts based on the ACCOUNTDISABLE flag, and maps users to organizations/roles via LDAP groups.
release
-
Adds ability to disable MISP accounts synced from LDAP based on the
ACCOUNTDISABLEflag behind a new setting
v2.5.45 · Aug 2026
· source
· release history
-
Adds LDAP sync of MISP accounts via the
User check_validitytask, schedulable as an admin task. v2.5.45 · Aug 2026 · source · release history
Event Template Submodule shipped Provides a managed library of starter event templates with auto-update capabilities.
release
-
New
misp-event-templatessubmodule provides a managed library catalogue with ten starter templates (e.g.ransomware-incident,credential-exposure,supply-chain-compromise) and first-touch auto-update. v2.5.37 · Apr 2026 · source · release history
example
-
Migrate all legacy templates to the new event-template format in bulk after upgrading.
app/Console/cake Admin migrateOldTemplatesv2.5.37 · Apr 2026 · source
Performance Benchmarking Tool shipped Provides a suite to track, document, and profile attribute search pipeline performance.
release
- Adds a benchmark suite and comparison tool for tracking and documenting attribute search pipeline performance. v2.5.35 · Mar 2026 · source · release history
- New purge function clears old SQL benchmark logs to keep logging data manageable. v2.5.16 · Jul 2025 · source · release history
Custom email template support shipped Allows overriding standard MISP email templates with custom HTML and text files.
release
-
Adds the ability to override standard email templates using custom files in
/var/www/MISP/app/View/Email/text/Custom/and/var/www/MISP/app/View/Email/html/Custom/. v2.4.158 · Apr 2022 · source · release history
example
-
Customize the forgot-password email body to match your organization's branding or include SOC contact details.
In the MISP console, go to Administration > Server Settings & Maintenance > MISP Settings and update the forgot password email text field.v2.5.32 · Jan 2026 · source
Event Deletion Trigger shipped suggested Enables workflow modules to execute actions immediately before an event is deleted.
Suggested capability: Response playbook automation. This is our guess, not confirmed.
release
-
New Event Deletion Trigger (
trigger-event-before-delete) to act on event deletion in workflows. v2.5.32 · Jan 2026 · source · release history
example
-
Act on event deletions in a workflow — e.g., to notify an external system or log deletions before they occur.
In the MISP console, go to Event Actions > Workflows, create a new workflow, and add the `trigger-event-before-delete` trigger as the starting node.v2.5.32 · Jan 2026 · source
Collections as first-class objects shipped Elevates collections to first-class citizen status, enabling structured organization of shared data and improved synchronization capabilities.
release
- Redacts creator user information in Collections data for non-site administrators. v2.5.28 · Dec 2025 · source · release history
- Adds Collections as a new first-class citizen object for organizing shared data v2.4.186 · Mar 2024 · source · release history
Event deletion recovery shipped Allows administrators to recover previously deleted events from the diagnostics page using event history.
release
- Adds validation for S3 bucket prefix when deleting events. v2.5.10 · May 2025 · source · release history
example
-
Recover a previously deleted event via the diagnostics page.
Go to Admin > Diagnostics > find 'recover-deleted-events' section and select the target event ID from history.v2.4.133 · Oct 2020 · source
User-level tag restrictions shipped Allows restricting tags to a single user in addition to existing organisation-level restrictions.
release
- Reworked attribute search now accepts parameters as query strings, uses a GET form, supports direct downloading of results, improves pagination, and aligns with restsearch behavior. v2.4.206 · Mar 2025 · source · release history
- Adds ability to restrict tags to a single user in addition to existing organisation-level restrictions v2.4.85 · Dec 2017 · source · release history
User login restrictions shipped Restricts user access to specific email domains at the organization level or via mandatory email-based OTP.
release
- Reworked Log Search with a modernized internal system, enhanced pagination, filter persistence, and improved UI field information. v2.4.203 · Jan 2025 · source · release history
- E-mail based OTP requires users to provide a token received via email at each new session login, accessible through the security settings. v2.4.125 · May 2020 · source · release history
Event report template variables shipped Enables administrators to define instance-wide template variables for use in event reports, accessible to all users.
release
- Introduces instance-wide template variables for reports, manageable only by site administrators but viewable and usable by all users. v2.4.201 · Dec 2024 · source · release history
- Introduces instance-wide template variables for reports, manageable only by site administrators but viewable and usable by all users. v2.5.3 · Dec 2024 · source · release history
Synchronization user visibility shipped Allows UI and API users to view bound synchronization users in the `/users` and `/servers` views.
Also counts toward: REST API
release
-
Adds UI and API export to display bound synchronization users in
/usersand/serversviews. v2.4.201 · Dec 2024 · source · release history -
Adds UI and API export to display bound synchronization users in
/usersand/serversviews. v2.5.3 · Dec 2024 · source · release history
Instance health verification shipped Provides unauthenticated mechanisms to verify MISP instance responsiveness, including a dedicated heartbeat endpoint and command-line checks.
Also counts toward: REST API
release
-
/users/heartbeatGET endpoint added for unauthenticated instance health checks returning HTTP 200 v2.4.194 · Jun 2024 · source · release history
example
-
Check if the MISP instance is responsive without needing API credentials or admin access.
curl -s -o /dev/null -w '%{http_code}' https://<misp_host>/users/heartbeatv2.4.194 · Jun 2024 · source
Event attribute modification tracking shipped Supports searching for events where specific attributes were modified within a given timeframe.
Also counts toward: REST API
release
-
Adds
first_seenandlast_seenfilters to the[objects]restsearchendpoint for time-bounded object queries v2.4.184 · Feb 2024 · source · release history
example
-
Query events where the attribute itself was modified within the last hour, distinct from the event creation time.
GET /attributes/restSearch?timestamp=3600&attribute_timestamp=truev2.4.119 · Dec 2019 · source
Log time-range filtering shipped Extends the log search capability to support specific time range parameters.
release
-
Adds time based filtering to logs via
timeparameter in log queries. v2.4.176 · Sep 2023 · source · release history - Extends log search API to support time range parameters. v2.4.103 · Mar 2019 · source · release history
Unauthenticated user registration queue shipped Allows unauthenticated users to request accounts, which land in an admin inbox for review before activation.
release
- Adds self-service password reset for users, enabling a login-screen link to enter email and receive a token with a 10-minute lifetime v2.4.173 · Jul 2023 · source · release history
-
self_registrationinbox allows unauthenticated registration requests to land in a queue for admin review, enabling ISACs and large communities to onboard members without manual user creation. v2.4.125 · May 2020 · source · release history
Enhanced dashboard widgets shipped Adds new configurable dashboard components including world maps, user/organization tickers, authentication lists, and event publishing charts.
release
-
latest Usersticker showing newly enrolled users v2.4.171 · May 2023 · source · release history - Published event line-chart widget v2.4.171 · May 2023 · source · release history
Event locking shipped Prevents concurrent editing conflicts by indicating when another user in the same organization is currently editing an event.
release
-
Adds
MISP.disable_event_locksserver setting to disable event lock checks. v2.4.157 · Mar 2022 · source · release history -
Adds
event lockfunctionality to show users if another user in the same organisation is editing the viewed event v2.4.93 · Jun 2018 · source · release history
Feed coverage comparison shipped Compares cached threat intelligence feeds against entire or subset other feeds for coverage analysis.
release
- Email notifications include a new configuration setting for event summaries only, excluding attributes and objects v2.4.145 · Jul 2021 · source · release history
-
feed comparefunctionality to compare cached feeds against entire or subset of other cached feeds for coverage analysis v2.4.104 · Mar 2019 · source · release history
External metadata lookup via Cerebrate shipped Integrates with external Cerebrate instances to retrieve and populate organization metadata during event creation and sharing group management.
release
- Adds the ability to use a Cerebrate instance as a lookup repository for organisation metadata within MISP events v2.4.136 · Jan 2021 · source · release history
example
-
Look up organisation metadata from a Cerebrate instance during event creation.
Configure MISP to point to your Cerebrate instance, then create an event and utilize the familiar preview/pull mechanism for organisation metadata.v2.4.136 · Jan 2021 · source
Indicator decay management shipped Automatically expires attributes based on custom or shared decay models.
release
-
Attributes'
last_seenfield now takes precedence overtimestampin decay computation v2.4.127 · Jun 2020 · source · release history - Introduces a new capability for decaying indicators to automatically expire attributes based on custom or shared decay models v2.4.116 · Sep 2019 · source · release history
Community ID correlation shipped Adds support for correlating network forensic flows using the community-id attribute type and associated object templates.
release
-
New object templates Netflow and Network connection included with support for the
community-idfield. v2.4.111 · Jul 2019 · source · release history -
community-idattribute type added for correlating network forensic flows from tools like Zeek, Suricata, Moloch, HELK, Elastic, and Corelight. v2.4.111 · Jul 2019 · source · release history
Warning list enforcement via API shipped suggested Allows enforcing warning lists on imported attributes via the `/attributes/add` endpoint.
Suggested capability: Threat indicator matching. This is our guess, not confirmed.
release
-
enforcewarninglistAPI option filters false-positives using new regex-based warning-list patterns v2.4.87 · Jan 2018 · source · release history -
Adds
/enforceWarninglist:1URL parameter and"enforceWarninglist":1key to/attributes/addfor filtering imported attributes via the API v2.4.85 · Dec 2017 · source · release history
Bulk attribute indexing actions shipped Allows users to perform bulk operations on multiple attributes directly from the event attribute index interface.
release
- Adds bulk actions in the Overmind event attribute index. v2.5.50 · Oct 2026 · source · release history
Detection rule object support shipped Adds new MISP objects for sharing detection rules, including Elastic, KQL, Kunai, and Splunk formats.
release
-
Adds
elastic-detection-rule,kql-analytics-rule,kunai-rule, andsplunk-ruleMISP objects for detection rule sharing.
v2.5.47 · Sep 2026
· source
· release history
Organization merging shipped Enables administrators to combine multiple organization accounts into a single unified entity through a dedicated UI workflow.
release
-
Adds an organisation merge feature in the UI.
v2.5.45 · Aug 2026
· source
· release history
Blocklist Action Module shipped Allows workflows to write event attributes to blocklist files with atomic writes and rollback support.
release
- New Workflows Blocklist action module writes event attributes to a blocklist file, with removal-by-tag, atomic writes with one-generation backup, and optional rolling filesystem snapshots. v2.5.38 · May 2026 · source · release history
Geolocation Migration Helper shipped Provides a CLI command to convert legacy templates to the new event-template format.
Also counts toward: Command-line interface
release
-
Migration helper
app/Console/cake Admin migrateOldTemplatesconverts legacy templates to the new event-template format, including handling for complex File / CnC objects. v2.5.37 · Apr 2026 · source · release history
Suricata Rule Support shipped Adds a dedicated Suricata IDS rule attribute type for first-class modeling and validation.
release
-
Adds a dedicated
suricataattribute type alongsidesnort, enabling first-class modeling and validation of Suricata IDS rules, with corresponding support in PyMISP. v2.5.37 · Apr 2026 · source · release history
Interactive terminal REPL for data browsing and management shipped Provides an interactive command-line interface to browse and manage cyber tool data without requiring a web browser.
Also counts toward: Command-line interface
example
-
Launch the interactive terminal REPL to browse and manage MISP data without a browser.
app/Console/cake CLI 1v2.5.36 · Apr 2026 · source
Correlation Dispatcher shipped Enables on-demand correlation loading per page rather than loading all correlations for an entire event.
release
- Introduces a new correlation dispatcher enabling per-page correlation loading instead of loading all correlations for an entire event at once. v2.5.35 · Mar 2026 · source · release history
Subdirectory deployment support shipped Adds configuration options to skip base URL coercion, enabling cleaner MISP deployments under a subdirectory path.
release
- Adds a new setting to skip base URL coercion, enabling cleaner deployments of MISP under a subdirectory. v2.4.202 · Dec 2024 · source · release history
Event report boilerplate reuse shipped suggested Allows analysts to reuse standard report elements, such as author names and TLP headers, across multiple event reports without re-entry.
Suggested capability: Incident case management. This is our guess, not confirmed.
example
-
Reuse analyst boilerplate (e.g. author name, TLP header) across all Event Reports without retyping it.
In the MISP console, go to Global Actions > My Profile > User Settings, define a template variable (e.g. `author: Jane Doe`), then reference it in any Event Report body as `{{ author }}`.v2.5.2 · Nov 2024 · source
Organizational context tagging shipped suggested Enables tagging phishing-page events with their DOM fingerprint to correlate structurally identical pages across instances.
Suggested capability: Threat indicator matching. This is our guess, not confirmed.
example
-
Tag a phishing-page event with its DOM fingerprint so analysts can correlate structurally identical pages across MISP instances.
In the event view, click 'Add Attribute', set Type to 'dom-hash', and paste the 32-character SHA-256 DOM fingerprint (e.g. from LookyLoo) as the value.v2.4.198 · Sep 2024 · source
Enhanced bookmark management shipped Allows users to add comments to bookmarks, making them visible in the index, dropdown titles, and edit views for better context.
release
- Bookmarks now support comments, visible in the bookmark index, dropdown menu titles, and add/edit views. v2.4.197 · Sep 2024 · source · release history
User organization identification shipped Allows exposing the requesting user's organization UUID in API response headers for better downstream tracking.
release
-
New
user_org_uuid_in_response_headerconfig option includes the requesting user's organization UUID in API response headers. v2.4.197 · Sep 2024 · source · release history
Disarm galaxy integration shipped Introduces the Disarm framework as a new galaxy cluster with Actor Types, Countermeasures, Detections, and Techniques for enriched tagging.
release
- New disarm galaxy available with Actor Types, Countermeasures, Detections, and Techniques clusters v2.4.183 · Jan 2024 · source · release history
Bulk event updates shipped Allows high-performance bulk event updates by bypassing duplicate validation checks.
release
-
Adds a
fast_updatemode to the/events/editendpoint to bypass duplicate validation for high-performance bulk updates v2.4.179 · Nov 2023 · source · release history
UI visibility for unpubished content shipped Highlights attributes and objects that are new or awaiting publication within the event view interface.
release
- Shows which attributes and objects are new and awaiting publication in the UI. v2.4.176 · Sep 2023 · source · release history
TAXII browser shipped Provides a UI component to browse TAXII servers, view collections, and inspect STIX object contents directly within the cyber tooling.
Also counts toward: STIX and TAXII
release
- Adds TAXII browser to view collections and browse STIX object contents at the taxii_servers/view/[id] endpoint v2.4.172 · Jun 2023 · source · release history
Microsoft Teams notification module shipped Adds a new webhook-based notification module specifically for Microsoft Teams.
release
- Adds new Microsoft Teams module based on the existing webhook module. v2.4.162 · Sep 2022 · source · release history
LinOTP authentication subsystem shipped Adds support for LinOTP one-time password authentication via system configuration.
release
-
Adds the
LinOTP.enablesystem setting to control the LinOTP authentication subsystem via configuration v2.4.156 · Mar 2022 · source · release history
MWDB malware sample push module shipped Adds a new export module to push malware samples directly to MWDB instances.
release
- New MWDB push module added for malware samples. v2.4.153 · Feb 2022 · source · release history
Social and personal relationship objects shipped Adds MISP object templates for social and personal relationships based on FOAF standards.
release
- New social and personal relationships based on FOAF relationships added to MISP objects. v2.4.153 · Feb 2022 · source · release history
Unified Kill Chain taxonomy shipped Adds the Unified Kill Chain framework as a new taxonomy option for tagging and analysis.
release
- New Unified Kill Chain taxonomy added. v2.4.153 · Feb 2022 · source · release history
VirusTotal collection export module shipped Adds a new MISP Module to export events into VirusTotal collections.
release
-
New
virustotal_collectionsexport module added for MISP Modules. v2.4.153 · Feb 2022 · source · release history
Feed organization context shipped Allows feed indexes to specify an organizational context for all events generated by CSV or freetext feeds.
release
-
Feed index refactoring adds the ability to select an
orgc_idfor CSV/freetext feeds so all generated events carry that organization context. v2.4.125 · May 2020 · source · release history
Dashboard template management shipped Enables users to save, load, and share dashboard configurations via the UI or JSON files.
Also counts toward: JSON data export
release
- Supports saving and sharing Dashboard templates via MISP UI or JSON configuration files. v2.4.123 · Mar 2020 · source · release history
Backend configuration reloading shipped Enables background workers to reload server-wide configurations on each job execution without requiring a full server restart.
release
- Background workers now reload server-wide configurations on each job execution instead of only at startup, allowing live setting changes to take effect without restarts. v2.4.121 · Feb 2020 · source · release history
Custom SSL/TLS certificate support shipped Allows overriding the default CA bundle with a custom one for outbound connections.
release
- Allows overriding MISP's default CA bundle with a custom one v2.4.117 · Oct 2019 · source · release history
Publish filter management shipped Allows users to create nested boolean rule systems to restrict alert e-mails by tags and publishing organisations.
release
- Adds Publish Filters to user settings to create nested boolean rule systems restricting alert e-mails by tags and publishing organisations v2.4.117 · Oct 2019 · source · release history
Redis diagnostics shipped Exposes Redis configuration diagnostics directly within the MISP UI diagnostics page.
release
- Adds Redis configuration diagnosis directly from the MISP UI diagnostics page v2.4.117 · Oct 2019 · source · release history
ATT&CK sightings export shipped Enables exporting MISP sightings in the MITRE ATT&CK sightings format.
release
- Adds the ability to export MISP sightings in the MITRE ATT&CK sightings format v2.4.116 · Sep 2019 · source · release history
CWS attribute support shipped Adds support for Common Weakness Scoring (CWS) attributes to identify software weaknesses in events.
example
-
Add a new CWS (Common Weakness Scoring) attribute to an existing event.
# Create the event ID first if needed, then add attribute # Using PyMISP or API with new type curl -X POST "https://misp.local/events/addAttribute/12345" \ -H 'Authorization: YOUR_API_KEY' \ -d '{…v2.4.112 · Aug 2019 · source
Unified correlation search shipped Retrieves event correlations and sightings in a single search operation to reduce API round trips.
example
-
Get event correlations and sightings in a single search to reduce round trips.
curl -X GET "https://misp.local/attributes/restSearch" \ -H 'Authorization: YOUR_API_KEY' \ -H 'Content-Type: application/json' \ -d '{ "search": {"category": "Network activity"}, "includeSightings":…v2.4.112 · Aug 2019 · source
YARA rule export shipped suggested Generates YARA rules and YARA-JSON formats directly from existing MISP attributes.
Suggested capability: Threat indicator matching. This is our guess, not confirmed.
Also counts toward: JSON data export
release
-
Native
yaraandyara-jsonexport formats for generating YARA rules from existing MISP attributes v2.4.107 · May 2019 · source · release history
Programmatic password management shipped Exposes the password change capability to the API for programmatic user credential updates.
release
-
Exposes
change_pwto the API for changing passwords programmatically. v2.4.103 · Mar 2019 · source · release history
Mass-action unpublishing shipped Allows users to simplify the process of unpublishing events or attributes via a dedicated UI action.
release
-
Adds a new
unpublish actionin the UI to simplify unpublishing events/attributes v2.4.101 · Jan 2019 · source · release history
Result count exposure shipped Exposes the total number of results from search operations via an HTTP response header.
Also counts toward: REST API
release
-
Exposes the result count from restSearch API responses via the
x-result-countresponse header v2.4.98 · Nov 2018 · source · release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
No command matches.
| option | found in | since | description |
|---|
Values are placeholders taken from each option’s declared default. Nothing is executed here — the output shown is a recording of a run that already happened.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
- Community health
-
Contributor trend distinct committers, this year against last
-
Maintainer concentration bus factor now against a year ago
-
Issue backlog trend issues closed per issue opened, 12 months
-
Responsiveness median time to a maintainer’s first reply
Nine scores for MISP, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail MISP puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Releases
179 entries
No entries match these filters.
- October 20261
- September 20263
- August 20261
- July 20261
- June 20267
- May 20261
- April 20266
- March 20263
- January 20261
- December 20254
- November 20254
- October 20252
- September 20251
- August 20252
- July 20252
- June 20254
- May 20256
- March 20252
- February 20252
- January 20254
- December 20244
- November 20242
- October 20243
- September 20242
- August 20242
- June 20242
- May 20241
- April 20243
- March 20243
- February 20241
- January 20241
- December 20232
- November 20231
- October 20231
- September 20232
- August 20231
- July 20232
- June 20231
- May 20231
- April 20231
- March 20231
- February 20231
- December 20221
- November 20222
- October 20221
- September 20222
- August 20222
- May 20221
- April 20221
- March 20223
- February 20221
- December 20211
- November 20211
- October 20211
- August 20211
- July 20212
- June 20211
- May 20211
- April 20212
- March 20211
- February 20212
- January 20212
- December 20201
- November 20201
- October 20201
- September 20202
- August 20201
- July 20201
- June 20203
- May 20201
- April 20201
- March 20201
- February 20202
- January 20201
- December 20191
- November 20191
- October 20191
- September 20192
- August 20193
- July 20192
- June 20192
- May 20191
- April 20191
- March 20193
- February 20191
- January 20192
- December 20181
- November 20181
- October 20182
- September 20181
- August 20181
- June 20182
- May 20181
- April 20181
- March 20181
- February 20181
- January 20182
- December 20172
- November 20171
- October 20171
- September 20171
Project health
Issue, contributor and maintainer activity in MISP/MISP, 2023-10 – 2026-09, as of 2026-09-25. Twelve-month figures first; the trend lines run the whole window.
- Contributors 70 +18 vs prior 12 months
- Maintainers 4 +4 joined · −5 left, last 12 months
- Bus factor 1 committers behind half the commits
- Community-filed 93% of issues opened, last 12 months
- Median time to close 42 days first maintainer reply 7.3 days
- Open backlog 2,690 of 7,032 issues ever filed
- Issues opened / month 6 · 0 communitymaintainers
- Open backlog 2,690
- Contributors / month 12
- Commits / month 260
- Stars 6,536
- bugs 22%
- features 22%
- questions 8%
- other 48%
Counts from the project's public repository and git history; no individuals are identified. Maintainers are the committers covering 80% of the last year's commits. how we measure this
Articles
1 article · updated Nov 4, 2026Where MISP turns up in what others publish: how-tos, attack reports that name it, and incident write-ups. A row says why it is here and quotes where the article names it; the link goes to the publisher.
Tutorials & guides 1
-
Threat Intelligence: MISP Lab Setup
MISP is an open-source Threat intelligence and sharing platform (formerly known as Malware Information Sharing Platform) that is used for collecting, storing distributing and sharing cybersecurity indicators and threats…
2 more quotes
MISP provides facilities to support the exchange of information but also the consumption of information by network intrusion detection systems (NIDS), a Log-based intrusion detection system (LIDS), but also by log…
MISP provides storage of technical and non-technical information about seen malware and attacks.
Libraries its release ships
What its latest release locks, checked against known advisories.None of its release's images build from a lockfile we can read.
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →