Prowler is an open-source cloud security platform, free to use, that runs security and compliance checks against cloud environments from the command line, with a web app and a managed cloud service available for teams that want that instead. It covers AWS, Azure, GCP, and a long list of other providers spanning SaaSSaaSSoftware delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally. platforms like M365, Okta, and GitHub, Kubernetes clusters, and container images, mapping checks to frameworks such as CISCISA nonprofit that publishes consensus-based configuration benchmarks and controls for hardening operating systems, cloud environments, and software; cyber tools use it as a ready-made compliance baseline. benchmarks, DORA, and DISA STIGs. This makes it a fit for cloud security and compliance teams who need audit evidence across multiple providers rather than a single-cloud tool. It sits in the cloud security posture managementcloud security posture managementCloud security posture management, checking cloud resources for risky settings and policy violations. It helps teams find exposed services, overly broad permissions and other configuration gaps. space, competing with commercial CSPMCSPMCloud security posture management, checking cloud resources for risky settings and policy violations. It helps teams find exposed services, overly broad permissions and other configuration gaps. products but staying free and self-run. Started in 2016, it now has over 500 contributors and a release roughly every two weeks, with the last one 15 days ago.
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.
Which of my cloud accounts fail a compliance benchmark like CIS or DORA before an auditor finds out?
runs the mapped checks against the live environment and reports each control as pass or fail, tied back to the specific framework requirement it maps to
Are my SaaS tenants and identity providers configured as securely as my cloud infrastructure?
runs the same kind of check-based audit against M365, Google Workspace, Okta, and GitHub, naming the setting that fails and the service it belongs to
Which container images or Kubernetes clusters are running with settings that violate basic hardening rules?
inspects image layers and cluster resources for issues like missing resource limits, floating image tags, or disabled probes and reports each violation by resource
Have I already fixed the misconfiguration a new check was written for?
scores every existing account, project, or tenant against newly added checks the next time a scan runs, so a resolved issue shows as passing and an unresolved one shows up immediately
Is one cloud account or subscription drifting from the security posture of the others?
scans every configured provider account under one run and reports results per account, so an outlier fails checks the rest pass
Can I show an auditor evidence for a specific regulation instead of a generic security score?
groups findings under the named framework's own control numbers, so results can be handed over mapped to CIS, DORA, or DISA STIG language instead of the tool's own labels
134 capabilities
across 12 capability groups
· 4 backed by code, an API document or a real run
Built from Prowler's releases, docs, README and our own runs.
“Seen” marks the month we first spotted a release the vendor didn't date.
Group names and tags are our labels.
+Secret scanning engineshippedScans code and configuration files for hardcoded secrets fully offline, with false-positive suppression and optional live validation to promote confirmed leaks to critical severity.9 releases · 1 other source · first seen Jul 2026▸
Also counts toward: Command-line interface, Offline mode
release
9 total
Adds batch_job_definition_no_secrets check for AWS, scanning Batch job definition environment variables and command parameters for hardcoded secrets.
5.39.0 · Aug 2026
· source
· release history
Adds awslambda_layer_no_secrets_in_content check for AWS, scanning Lambda layer package content for hardcoded secrets.
5.39.0 · Aug 2026
· source
· release history
Adds glue_catalog_connection_no_secrets check to detect secrets in Glue Data Catalog connection properties.
5.37.0 · Aug 2026
· source
· release history
Adds codecommit_repository_no_secrets check (and new codecommit service) to scan files at the tip of each repository's default branch for hardcoded secrets.
5.37.0 · Aug 2026
· source
· release history
New sagemaker_notebook_instance_no_secrets check scans SageMaker notebook instance OnCreate and OnStart lifecycle scripts for hardcoded API keys, passwords, tokens, and connection strings.
5.36.0 · Jul 2026
· source
· release history
New AWS check amplify_app_no_secrets_in_environment: scans Amplify app and branch environment variables and build settings (buildSpec) for hardcoded secrets using Kingfisher.
5.34.0 · Jul 2026
· source
· release history
example
Validate discovered secrets against live provider APIs so only working credentials are flagged critical — useful in CI to triage real leaks from noise.$ prowler aws --scan-secrets-validate
5.32.0 · Jul 2026
· source
+GitHub Actions workflow scanningshippedStatically scans GitHub Actions workflow files for CI/CD risks including script injection and overly permissive tokens using zizmor.3 releases · first seen Apr 2026▸
New organization_actions_pull_request_approval_disabled check (GitHub) verifies that organizations prevent GitHub Actions from creating and approving pull requests.
5.40.0 · Aug 2026
· source
· release history
New GitHub Actions service uses zizmor v1.24.1 to statically scan .github/workflows/*.yml for OWASP Top 10 CI/CD risks including script injection, overly permissive GITHUB_TOKEN, untrusted checkouts, and dangerous triggers.
5.25.0 · Apr 2026
· source
· release history
Harden-Runner enabled across GitHub Actions workflows to monitor and restrict outbound network traffic during CI runs.
5.23.0 · Apr 2026
· source
· release history
+Secret scanning false-positive suppressionshippedSkips files matching configurable glob patterns when scanning for secrets to reduce false positives, such as .NET dependency manifests.2 releases · first seen Jul 2026▸
+IaC scanning for pre-deployment securityshippedScans Infrastructure-as-Code files (Terraform, CloudFormation, ARM, Kubernetes YAML) and remote Git repositories for misconfigurations before deployment.7 releases · 2 other sources · first seen Jul 2025▸
Also counts toward: CI/CD pipeline integration, Command-line interface
release
7 total
IaC provider now emits SARIF via --output-formats sarif, enabling IaC misconfigurations to appear as annotations in GitHub Security → Code Scanning on PRs.
5.25.0 · Apr 2026
· source
· release history
Adds IaC supported formats and scanner documentation for the IaC provider.
5.16.0 · Dec 2025
· source
· release history
Adds external resource links to IaC findings for direct navigation to source code in Git repositories.
5.14.0 · Nov 2025
· source
· release history
Adds a new Infrastructure-as-Code (IaC) provider powered by Trivy for scanning Terraform, CloudFormation, Kubernetes manifests, Dockerfiles, Helm charts, Azure ARM templates, and secrets before deployment.
5.14.0 · Nov 2025
· source
· release history
Uses branch name as the region identifier for IaC findings.
5.14.0 · Nov 2025
· source
· release history
IaC provider now supports scanning remote Git repositories (public and private) via --scan-repository-url, enabling direct CI/CD pipeline integration.
5.9.0 · Jul 2025
· source
· release history
example
Scan IaC files in a remote private Git repo from a CI/CD pipeline without cloning it locally first.$ prowler iac --scan-repository-url https://github.com/user/repo.git
5.9.0 · Jul 2025
· source
Scan local IaC files (Terraform, CloudFormation, Kubernetes YAML, etc.) for misconfigurations before deploying — shift-left security in CI/CD or local workflows.$ prowler iac
5.8.0 · Jul 2025
· source
+Kubernetes workload configuration checksshippedChecks Kubernetes workloads for CPU and memory limits, fixed image tags, liveness probes, and readiness probes.6 releases · first seen Jun 2026▸
New Kubernetes check core_readonly_root_filesystem_enabled: verifies every container in each Pod explicitly sets readOnlyRootFilesystem: true in its security context.
5.34.0 · Jul 2026
· source
· release history
New Kubernetes check core_minimize_hostpath_volume_mounts: detects Pods that use hostPath volumes.
5.34.0 · Jul 2026
· source
· release history
New Kubernetes check core_minimize_hostpath_volume_mounts: detects Pods that use hostPath volumes.
5.34.0 · Jul 2026
· source
· release history
New Kubernetes check core_readonly_root_filesystem_enabled: verifies every container in each Pod explicitly sets readOnlyRootFilesystem: true in its security context.
5.34.0 · Jul 2026
· source
· release history
New Kubernetes checks for CPU/memory limits and requests, fixed image tags, liveness probes, and readiness probes.
5.31.0 · Jun 2026
· source
· release history
New Kubernetes checks for container resource governance: CPU limits, CPU requests, memory limits, memory requests, fixed image tags, liveness probes, and readiness probes.
5.31.0 · Jun 2026
· source
· release history
+CI/CD pipeline scanningshippedIntegrates into GitHub Actions workflows to scan IaC, export findings as SARIF, and push results to the cyber tool platform.1 release · 1 other source · first seen Apr 2026▸
New official GitHub Action prowler-cloud/prowler@5.25 runs Prowler scans in CI, with optional SARIF upload to GitHub Code Scanning and push to Prowler Cloud.
5.25.0 · Apr 2026
· source
· release history
example
Drop Prowler into a GitHub Actions workflow to scan IaC, upload findings as SARIF annotations to Code Scanning, and push results to Prowler Cloud.$ - uses: prowler-cloud/prowler@5.25 with: provider: iac output-formats: sarif json-ocsf upload-sarif: true flags: --severity critical high
5.25.0 · Apr 2026
· source
+Log parsing and normalization3 featuresLogs and telemetrysince 2023▸
+Scan output format updatesshippedUpdates OCSF output format to v1.3.0, renames and standardizes timestamp fields, and removes deprecated container objects.6 releases · first seen Nov 2024▸
Shared capability: Log parsing and normalization
release
Populates finding_info.analytic and finding_info.attacks fields in OCSF output with Prowler rule and MITRE ATT&CK data.
5.37.0 · Aug 2026
· source
· release history
Generates ASFF output for AWS providers when Security Hub integration is enabled.
5.11.0 · Aug 2025
· source
· release history
The OCSF output container object is removed.
4.5.0 · Nov 2024
· source
· release history
The OCSF output field finding_info.created_time changes format from a timestamp to a unix timestamp.
4.5.0 · Nov 2024
· source
· release history
Updates OCSF output format to v1.3.0, adding finding_info.created_time_dt, finding_info.name, finding_info.types, time_dt, metadata.product.uid, and metadata.profiles fields.
4.5.0 · Nov 2024
· source
· release history
The OCSF output field event_time is renamed to time and its format changes from a timestamp to a unix timestamp.
4.5.0 · Nov 2024
· source
· release history
+Unix timestamp output supportshippedEnables Unix timestamps in all scan outputs for easier log parsing and time-series correlation.1 release · 1 other source · first seen Oct 2023▸
Shared capability: Log parsing and normalization
Also counts toward: Command-line interface
release
Prowler outputs now support Unix timestamps via the --unix-timestamp flag.
3.10.0 · Oct 2023
· source
· release history
example
Enable Unix timestamps in all outputs for easier log parsing and time-series correlation$ prowler aws --unix-timestamp -o output.json
3.10.0 · Oct 2023
· source
+Non-existent resource standardizationshippedStandardizes ARN and ID patterns for non-existent resources in scan outputs.1 release · first seen Nov 2024▸
Shared capability: Log parsing and normalization
release
Introduces standardized Unknown ARN and ID patterns (arn:<partition>:<service>:<region>:<account-id>:resource-type/unknown) for non-existent resources instead of mocked values.
4.6.0 · Nov 2024
· source
· release history
+Container image provider scanningshippedScans container images by tag, digest, or registry enumeration across OCI registries, Docker Hub, and Amazon ECR for vulnerabilities using Trivy.8 releases · 2 other sources · first seen Mar 2026▸
Adds support for TRIVY_CACHE_DIR environment variable in the Image provider, allowing reuse of Trivy vulnerability database across scans or use of a pre-populated DB with TRIVY_SKIP_DB_UPDATE=true
5.42.0 · Sep 2026
· source
· release history
Honors TRIVY_CACHE_DIR in the Image provider so the Trivy vulnerability database is downloaded once and reused across scans; pairing it with TRIVY_SKIP_DB_UPDATE=true enables air-gapped image scanning against a pre-populated database.
5.42.0 · Sep 2026
· source
· release history
Adds --registry-insecure flag propagation to Trivy via TRIVY_INSECURE, enabling pull and scan of images behind self-signed certificates on trusted internal registries.
5.41.0 · Sep 2026
· source
· release history
Adds support for on-premises registries by allowing the Image Provider to reach private networks via the PROWLER_IMAGE_PROVIDER_ALLOWED_PRIVATE_NETWORKS environment variable
5.41.0 · Sep 2026
· source
· release history
Propagates the --registry-insecure flag to Trivy via TRIVY_INSECURE to allow image pulls from self-signed certificate registries
5.41.0 · Sep 2026
· source
· release history
Image provider registry scans now enumerate repositories in parallel, skip non-image OCI artifacts (Helm charts, cosign signatures, SBOM attestations), and continue scanning remaining images when Trivy fails on a single image.
5.41.0 · Sep 2026
· source
· release history
docs
Skipping TLS verification disables certificate validation for registry connections, including the Trivy image pull ( TRIVY_INSECURE ). Use this flag only for trusted internal registries with self-signed certificates.
docs update · Sep 2026
· source
example
Scan container images in an air-gapped environment by pointing Prowler at a pre-populated Trivy database and skipping the download.$ export TRIVY_CACHE_DIR=/mnt/trivy-db export TRIVY_SKIP_DB_UPDATE=true prowler image myregistry.internal/myapp:latest
5.42.0 · Sep 2026
· source
+Container image vulnerability scanningshippedRuns Grype alongside Trivy as container image security gates, blocking on fixable high and critical vulnerability findings.1 release · first seen Aug 2026▸
Grype now runs alongside Trivy across container-image security gates, blocking on fixable high and critical findings.
5.38.0 · Aug 2026
· source
· release history
+Encryption at rest2 featuresData discovery and protectionsince 2026▸
+AWS Step Functions encryption checkshippedFlags Step Functions state machines not encrypted with a customer-managed KMS key.2 releases · first seen Jul 2026▸
Shared capability: Encryption at rest
release
New AWS check stepfunctions_statemachine_encrypted_with_cmk: flags Step Functions state machines not using a customer-managed KMS key.
5.32.0 · Jul 2026
· source
· release history
New AWS check stepfunctions_statemachine_encrypted_with_cmk: detects Step Functions state machines not using a customer-managed KMS key.
5.32.0 · Jul 2026
· source
· release history
+GCP KMS key rotation checksshippedChecks GCP KMS keys to confirm rotation is enabled and that the rotation period does not exceed 90 days.2 releases · first seen Jun 2026▸
Shared capability: Encryption at rest
release
Splits GCP kms_key_rotation_enabled into two focused checks: one for rotation being enabled and one enforcing a maximum 90-day rotation period.
5.30.0 · Jun 2026
· source
· release history
GCP kms_key_rotation_enabled is split into two focused checks: one for rotation being enabled and one enforcing a maximum 90-day rotation period.
5.30.0 · Jun 2026
· source
· release history
+Data access governance2 featuresData discovery and protectionsince 2023▸
+OCI identity and access checksshippedChecks OCI identity configuration to ensure storage service-level admin accounts lack delete permissions per CIS control 1.15.3 releases · first seen Jun 2026▸
Shared capability: Data access governance
release
OCI provider setup no longer requires a region — SDK handles region discovery automatically, simplifying onboarding.
5.36.0 · Jul 2026
· source
· release history
New OCI check: identity_storage_service_level_admins_scoped (CIS 3.1 control 1.15) ensures storage admins exclude delete permissions.
5.31.0 · Jun 2026
· source
· release history
New OCI check: identity_storage_service_level_admins_scoped (CIS 3.1 control 1.15) ensuring storage admins exclude delete permissions.
5.31.0 · Jun 2026
· source
· release history
+AWS S3 object-level public access checkshippedSpot-checks S3 object ACLs for public grants to AllUsers or AuthenticatedUsers as an opt-in check.2 releases · 1 other source · first seen Aug 2023▸
Shared capability: Data access governance
release
New AWS check s3_bucket_object_public: spot-checks object ACLs for public grants (AllUsers/AuthenticatedUsers); opt in via s3_bucket_object_public_enabled config option.
5.32.0 · Jul 2026
· source
· release history
New AWS check s3_bucket_object_public: spot-checks a configurable sample of object ACLs per bucket and flags objects granted to AllUsers or AuthenticatedUsers; opt in via s3_bucket_object_public_enabled configuration option.
5.32.0 · Jul 2026
· source
· release history
example
Scan AWS S3 specifically for public read/write ACL misconfigurations.$ prowler aws --service s3
3.8.0 · Aug 2023
· source
+Issues grouping and triage viewshippedGroups scan findings into issues with verdicts, verdict filters, and scoped finding evidence in Prowler Cloud for streamlined triage.2 releases · first seen Oct 2026▸
Shared capability: Vulnerability prioritization
release
Prowler's Issues list now leads with the verdict, shows the attack path under each title, and adds a Why column with five evidence legs; the menu entry is renamed to Exploitability issues.
5.47.0 · Oct 2026
· source
· release history
Adds an Issues page and overview cards in Prowler Cloud, grouping scan findings into issues with verdicts, verdict filters, accessible issue details, and scoped finding evidence.
5.46.0 · Oct 2026
· source
· release history
+Log search1 featureLogs and telemetrysince 2025▸
+Findings API time-window filteringshippedFilters findings via the API using full ISO 8601 timestamps on inserted-at and updated-at fields for precise time-window queries.5 releases · 1 other source · first seen Jan 2025▸
Shared capability: Log search
release
API /api/v1/findings endpoint accepts full ISO 8601 timestamps on filter[inserted_at__gte], filter[inserted_at__lte], filter[updated_at__gte], and filter[updated_at__lte] filters for precise time-window queries.
5.32.0 · Jul 2026
· source
· release history
Adds full-timestamp precision to /api/v1/findings filters: filter[inserted_at__gte], filter[inserted_at__lte], filter[updated_at__gte], and filter[updated_at__lte] now accept ISO 8601 timestamps for narrow time-window queries.
5.32.0 · Jul 2026
· source
· release history
Adds GET /findings/latest endpoint to retrieve the latest new failed findings
5.8.1 · Jul 2025
· source
· release history
Findings API endpoints now require at least one date filter when retrieving all findings.
5.3.0 · Feb 2025
· source
· release history
New /findings/metadata API endpoint retrieves dynamic filter information for findings.
5.1.3 · Jan 2025
· source
· release history
example
Query findings inserted within a precise time window to feed a shift-handoff report or SIEM alert.$ curl --globoff 'http://localhost:8080/api/v1/findings?filter[inserted_at__gte]=2026-07-01T06:12:18Z&filter[inserted_at__lte]=2026-07-02T19:25:55Z' -H 'Authorization: Bearer <YOUR_TOKEN>' -H 'Accept:…
5.32.0 · Jul 2026
· source
+Log routing1 featureLogs and telemetrysince 2023▸
+Automated findings distributionshippedProvides native integration to automatically forward scan findings to AWS Security Hub and Jira projects for centralized tracking and reporting.6 releases · 1 other source · first seen Feb 2023▸
Shared capability: Log routing
Also counts toward: Ticketing integration
release
Jira issues created from findings now carry labels prowler, prowler-<provider>, prowler-<severity>, prowler-<check-id>, and prowler-finding-<finding-uid> for JQL filtering and automation matching.
5.41.0 · Sep 2026
· source
· release history
Adds DJANGO_UI_BASE_URL API environment variable; when set, Jira issues created from findings include a direct link back to the finding filtered by its UID.
5.41.0 · Sep 2026
· source
· release history
Adds stable Jira issue labels (prowler, prowler-<provider>, prowler-<severity>, prowler-<check-id>, prowler-finding-<finding-uid>) and a back-link to the Prowler finding for every Jira integration issue
5.41.0 · Sep 2026
· source
· release history
Sends Prowler findings directly to JIRA projects as Task issues, with labels, finding URLs, tenant info, and color-coded severity for MANUAL findings.
5.12.0 · Sep 2025
· source
· release history
Adds AWS Security Hub integration to automatically forward Prowler findings to Security Hub, with support for session, profile, role, and static credential authentication.
5.11.0 · Aug 2025
· source
· release history
Adds --skip-sh-update CLI argument to skip the AWS Security Hub update step during scan execution
3.2.1 · Feb 2023
· source
· release history
example
Execute a Prowler scan against AWS without pushing results to or updating AWS Security Hub, useful for environments where SH is disabled or restricted.$ prowler aws --skip-sh-update
3.2.1 · Feb 2023
· source
+Distributed tracing1 featureLogs and telemetrysince 2026▸
+API performance tracingshippedEnables configurable Sentry tracing for the API to monitor production transaction performance and capture detailed execution traces.1 release · 1 other source · first seen Apr 2026▸
Shared capability: Distributed tracing
release
New DJANGO_SENTRY_TRACES_SAMPLE_RATE env var enables Sentry performance tracing for the Prowler API (default 0.02).
5.24.4 · Apr 2026
· source
· release history
example
Enable Sentry performance tracing for the API at a higher sample rate to capture more transaction traces in production.$ DJANGO_SENTRY_TRACES_SAMPLE_RATE=0.1 <your API start command>
5.24.4 · Apr 2026
· source
+SAML SSO1 featureIdentity and accesssince 2025▸
+SAML SSO role provisioningshippedProvisions user roles via SAML SSO userType attribute, preserving existing roles when the attribute is absent.6 releases · first seen Jul 2025▸
Shared capability: SAML SSO
Also counts toward: Role-based access control, Single sign-on, SAML SSO
release
SAML SSO now supports one primary email domain plus up to 19 additional domains under a single Identity Provider configuration and a single stable ACS URL (Prowler Cloud/Private Cloud).
5.38.0 · Aug 2026
· source
· release history
Users table in Prowler Cloud now shows each account's sign-in methods as tags, including email/password, Google, GitHub, SAML with linked domains, and Partner SSO.
5.38.0 · Aug 2026
· source
· release history
Allows a single SAML configuration to authorize up to 19 additional email domains alongside the primary domain
5.38.0 · Aug 2026
· source
· release history
SAML SSO userType attribute is now optional; missing or blank values preserve existing user roles rather than applying a fallback role.
5.31.0 · Jun 2026
· source
· release history
Optional SAML SSO userType attribute: when absent or blank, Prowler preserves existing user roles instead of applying a fallback role.
5.31.0 · Jun 2026
· source
· release history
Introduces SAML-based Single Sign-On via a new Sign in with SSO login option, supporting Okta and any SAML-compatible identity provider.
5.9.0 · Jul 2025
· source
· release history
+MCP server1 featureInterfaces and integrationssince 2025▸
+Prowler MCP ServershippedExposes Prowler capabilities as MCP tools for AI agents, covering findings triage, scan scheduling, alert rules, integrations, users, roles, and provider management.19 releases · 4 other sources · first seen Oct 2025▸
Prowler's MCP Server now annotates every tool with readOnlyHint and destructiveHint so MCP clients can distinguish read-only listing calls from writes; mute rule and mutelist writes are marked destructive.
5.47.0 · Oct 2026
· source
· release history
Adds MCP Server support for partial scans: prowler_trigger_scan accepts a resource_uids argument, and prowler_list_scans / prowler_get_scan return is_partial, with an is_partial filter on prowler_list_scans.
5.44.0 · Sep 2026
· source
· release history
Adds prowler_trigger_scan MCP tool support for a resource_uids argument to launch partial scans, and exposes is_partial on prowler_list_scans and prowler_get_scan with an is_partial filter on prowler_list_scans.
5.44.0 · Sep 2026
· source
· release history
Improves Prowler MCP Server tool failure reporting to use isError: true with explanation in content instead of wrapping errors in a successful result object
5.41.0 · Sep 2026
· source
· release history
MCP server tools now report failures as proper MCP tool execution errors (isError: true) instead of successful responses carrying an {"error": ...} payload; affects prowler_docs_search, prowler_docs_get_document, prowler_hub_get_check_code, prowler_hub_get_check_fixer, and…
5.41.0 · Sep 2026
· source
· release history
Adds eight organization MCP tools to the Prowler Cloud MCP server, enabling agents to onboard and manage entire AWS Organizations, GCP organizations, and Azure tenant root management groups end to end (Cloud/Private Cloud only).
5.39.0 · Aug 2026
· source
· release history
docs
runs on your own machine or infrastructure. The Cloud MCP Server additionally provides the prowler_cloud_* tools for Prowler Cloud-specific features: , and Scan Configurations.
docs update · Oct 2026
· source
Connect Claude Code to the Prowler Cloud MCP Server at https://mcp.prowler.com/mcp . Where Claude Code Runs Claude Code runs in two places. Both read the same configuration file, so you set it up once from a terminal and it works in both.
docs update · Jul 2026
· source
example
Install the Prowler Claude Code plugin to let Claude drive compliance assessments against your Prowler Cloud-connected account.$ /plugin marketplace add prowler-cloud/prowler /plugin install prowler@prowler-plugins
5.28.0 · May 2026
· source
Query daily aggregated findings by severity over time via the new API endpoint to track posture trends in a SIEM or dashboard.$ curl -s -H "Authorization: Bearer <token>" 'https://<prowler-api>/api/v1/overviews/findings_severity/timeseries'
5.15.0 · Dec 2025
· source
+Other / not yet classified113 featuresFeatures we have not matched to a capability yet. A suggested match is marked.▸
+CIS and regulatory compliance frameworksshippedProvides built-in CIS benchmarks for AWS, M365, Azure, GCP, GitHub, and Kubernetes, plus CIS Controls v8.1 as a universal compliance framework.69 releases · 11 other sources · first seen Jul 2017▸
release
69 total
Prowler adds iam_subscription_owners_between_2_and_3 check for Azure to verify each subscription has between two and three principals with the Owner role, including owners inherited from management groups, mapped to CIS 5.0 and 6.0.
5.47.0 · Oct 2026
· source
· release history
Prowler adds network_application_gateway_waf_enabled and network_application_gateway_http2_enabled checks for Azure Application Gateways and their WAF policies, mapped to CIS 5.0 and 6.0.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
5.47.0 · Oct 2026
· source
· release history
Adds fedramp_20x_ksi_2026 universal compliance framework covering the 46 FedRAMP Key Security Indicators across AWS, Azure, GCP, Kubernetes, and M365 from a single definition, replacing the pilot per-provider frameworks.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
5.43.0 · Sep 2026
· source
· release history
Introduces fedramp_20x_ksi_2026 framework covering AWS, Azure, GCP, Kubernetes and M365 for FedRAMP compliance
5.43.0 · Sep 2026
· source
· release history
Introduces fedramp_20x_frr_class_c_2026 framework binding 158 FedRAMP Class C rules for cloud providers
5.43.0 · Sep 2026
· source
· release history
Adds fedramp_20x_frr_class_c_2026 universal compliance framework covering 158 FedRAMP Class C provider rules across AWS, Azure, GCP, Kubernetes, and M365.
5.43.0 · Sep 2026
· source
· release history
docs
September 21, 2026 Compliance — FedRAMP 20x Consolidated Rules 2026 The FedRAMP 20x Phase One pilot frameworks ( fedramp_20x_ksi_low_aws fedramp_20x_ksi_low_azure fedramp_20x_ksi_low_gcp ) are replaced by two universal frameworks built from the FedRAMP Consolidated Rules for 2026, each covering AWS, Azure, GCP,…
docs update · Sep 2026
· source
example
10 total
List all available MongoDB Atlas security checks to understand what Prowler can assess before running a scan.$ prowler mongodb-atlas --list-checks
5.12.0 · Sep 2025
· source
Audit your GitHub organization's security posture against the CIS GitHub Benchmark v1.0.0 — useful for teams that want to enforce branch protection and MFA policies at scale.$ prowler github --list-checks
5.7.0 · May 2025
· source
Assess your AWS environment against the latest CIS AWS Foundations Benchmark v5.0.0 to identify gaps against updated best practices.$ prowler aws --compliance cis_5.0_aws
5.7.0 · May 2025
· source
Audit Azure subscriptions against the CIS Benchmark v2.0 standard$ prowler azure --compliance cis_2.0_azure
3.16.0 · Apr 2024
· source
Scan a Kubernetes cluster using a specific kubeconfig for CIS 1.8 compliance.$ prowler kubernetes --kubeconfig-file <kube.yaml>
4.0.0 · Apr 2024
· source
Run the new AWS Foundational Technical Review compliance framework against your AWS account.$ prowler aws --compliance foundational_technical_review_aws
3.15.0 · Mar 2024
· source
+AWS service security checks expansionshippedsuggestedExpands coverage to include specific AWS services and configurations such as EFS encryption, DynamoDB DAX, CloudWatch retention, Secrets Manager rotation, Shield Advanced, CodeArtifact publishing, and OpenSearch authentication.65 releases · 3 other sources · first seen Jan 2022▸
Suggested capability: Encryption at rest. This is our guess, not confirmed.
release
65 total
Adds wafv2_webacl_managed_rule_groups_enabled check, which verifies that WAFv2 Web ACLs reference at least one managed rule group.
5.46.0 · Oct 2026
· source
· release history
Adds cognito_user_pool_account_recovery_sms_not_preferred check, which verifies that Cognito user pools do not rank SMS first for account recovery.
5.46.0 · Oct 2026
· source
· release history
New check memorydb_cluster_in_transit_encryption_enabled verifies MemoryDB clusters have in-transit encryption (TLS) enabled.
5.41.0 · Sep 2026
· source
· release history
Adds agentcore_log_group_name_prefixes key to config.yaml to configure which CloudWatch log group prefixes the new cloudwatch_log_group_agentcore_data_protection_policy_enabled check evaluates.
5.41.0 · Sep 2026
· source
· release history
New check eks_cluster_vpc_cni_network_policy_enforced flags EKS clusters whose Amazon VPC CNI managed add-on does not enforce Kubernetes network policy.
5.41.0 · Sep 2026
· source
· release history
New check cloudwatch_log_group_agentcore_data_protection_policy_enabled verifies Bedrock AgentCore log groups have a CloudWatch Logs data protection policy masking sensitive data.
5.41.0 · Sep 2026
· source
· release history
example
Run the new WAFv2 and Bedrock checks together to audit whether Web ACLs and Bedrock guardrails meet baseline security requirements.$ prowler aws --checks wafv2_webacl_managed_rule_groups_enabled bedrock_guardrail_sensitive_information_filter_enforced bedrock_model_invocation_logging_text_data_enabled…
5.46.0 · Oct 2026
· source
List all 74 new checks available in this release to plan your expanded AWS security coverage.$ prowler aws --list-checks
4.4.0 · Sep 2024
· source
Run security checks for a cloud provider$ prowler <provider>
+Additional security checks coverageshippedExpands the available security checks to cover public exposure of AMIs, ECR repositories, and snapshots, alongside logging and encryption controls for RDS, ELB, Redshift, Macie, GuardDuty, CloudFront, Elasticsearch, S3, Route53, Lambda, API Gateway, EBS, SQS, SNS, ACM, KMS, and Trusted Advisor.48 releases · 3 other sources · first seen Jan 2018▸
release
48 total
Prowler's AWS security group internet exposure checks now treat CIDRs in a single ingress rule that together cover 0.0.0.0/0 or ::/0 (such as 0.0.0.0/1 plus 128.0.0.0/1) as open to the internet.
5.47.0 · Oct 2026
· source
· release history
Enables bootstrap STS failover via PROWLER_AWS_PARTITION environment variable for non-default partitions
5.43.0 · Sep 2026
· source
· release history
Adds seven new AWS checks: inspector2_coverage_scan_status_active, inspector2_coverage_recently_scanned (configurable via inspector2_max_days_since_last_scan, default 3), inspector2_active_findings_no_known_exploited_vulnerabilities, inspector2_active_findings_kev_within_due_date,…
5.43.0 · Sep 2026
· source
· release history
Adds inspector2:BatchGetFindingDetails to the Prowler additions policy and CloudFormation scan role so KEV checks can pull CISA Known Exploited Vulnerability data directly from Inspector without an external feed; missing permission reports MANUAL instead of a false FAIL.
5.43.0 · Sep 2026
· source
· release history
New check ecr_registry_enhanced_scanning_enabled verifies the ECR registry uses enhanced scanning (Amazon Inspector with continuous rescanning) instead of basic scanning.
5.41.0 · Sep 2026
· source
· release history
New check guardduty_ai_protection_enabled flags GuardDuty detectors without AI Protection for Bedrock, Bedrock AgentCore, and SageMaker AI CloudTrail data events.
5.41.0 · Sep 2026
· source
· release history
docs
Open-source cloud security platform that runs automated compliance and security checks across AWS, Azure, GCP, Kubernetes, and other providers via CLI, API, or
example
Scan an AWS ISO partition region that was previously unsupported without a hand-edited region file.$ prowler aws --region us-isob-east-1
5.42.0 · Sep 2026
· source
List supported services for provider$ prowler <provider> --list-services
+M365 Entra and Exchange security checksshippedFlags unowned privileged service principals, directory sync takeover risks, conditional access policy gaps, and mailbox domain misconfigurations in Microsoft 365 Entra and Exchange.27 releases · 1 other source · first seen Mar 2025▸
Also counts toward: Ticketing integration
release
27 total
Adds 20 new Microsoft 365 Entra ID checks for CIS Microsoft 365 Foundations Benchmark v7.0.0, covering password protection, default user permissions, Conditional Access, sessions and authentication methods, and PIM and access reviews.
5.39.0 · Aug 2026
· source
· release history
Adds entra_device_registration_join_restricted, entra_device_registration_max_devices_per_user_limited, entra_device_registration_global_admins_not_local_admins, entra_device_registration_registering_user_not_local_admin, entra_device_registration_laps_enabled, and…
5.38.0 · Aug 2026
· source
· release history
Grouped Jira workflows (Prowler Cloud/Private Cloud): send selected findings or Finding Groups to Jira as one grouped issue or separate issues, with deep links and filter context preserved.
5.36.0 · Jul 2026
· source
· release history
New Microsoft 365 checks: entra_directory_sync_object_takeover_blocked and entra_conditional_access_policy_no_deleted_object_references.
5.31.0 · Jun 2026
· source
· release history
New M365 checks: entra_directory_sync_object_takeover_blocked and entra_conditional_access_policy_no_deleted_object_references.
5.31.0 · Jun 2026
· source
· release history
New M365 check entra_service_principal_privileged_role_no_owners flags privileged service principals with no assigned owners.
5.30.0 · Jun 2026
· source
· release history
example
Run all new SharePoint external sharing and authentication checks against a Microsoft 365 tenant.$ prowler microsoft365 --service sharepoint
5.4.0 · Mar 2025
· source
+Lighthouse AI agentic assistantshippedProvides an AI assistant in Prowler Cloud that answers questions about findings, compliance posture, and risky resources using a configurable LLM provider, with persistent chat sessions and streaming.23 releases · 2 other sources · first seen Feb 2020▸
Also counts toward: Built-in AI assistant, Natural-language query
release
23 total
Enables Lighthouse AI to launch partial scans targeting specific resources for remediation confirmation.
5.44.0 · Sep 2026
· source
· release history
Adds PROWLER_IMAGE_PROVIDER_ALLOWED_PRIVATE_NETWORKS environment variable accepting a comma-separated list of IPs and CIDRs to allow the Image provider to reach on-premises registries while keeping all other non-public addresses blocked by the SSRF guard.
5.41.0 · Sep 2026
· source
· release history
Lighthouse AI answers now support thumbs-up/thumbs-down feedback with an optional free-text detail field, collected per answer directly in the chat.
5.40.0 · Aug 2026
· source
· release history
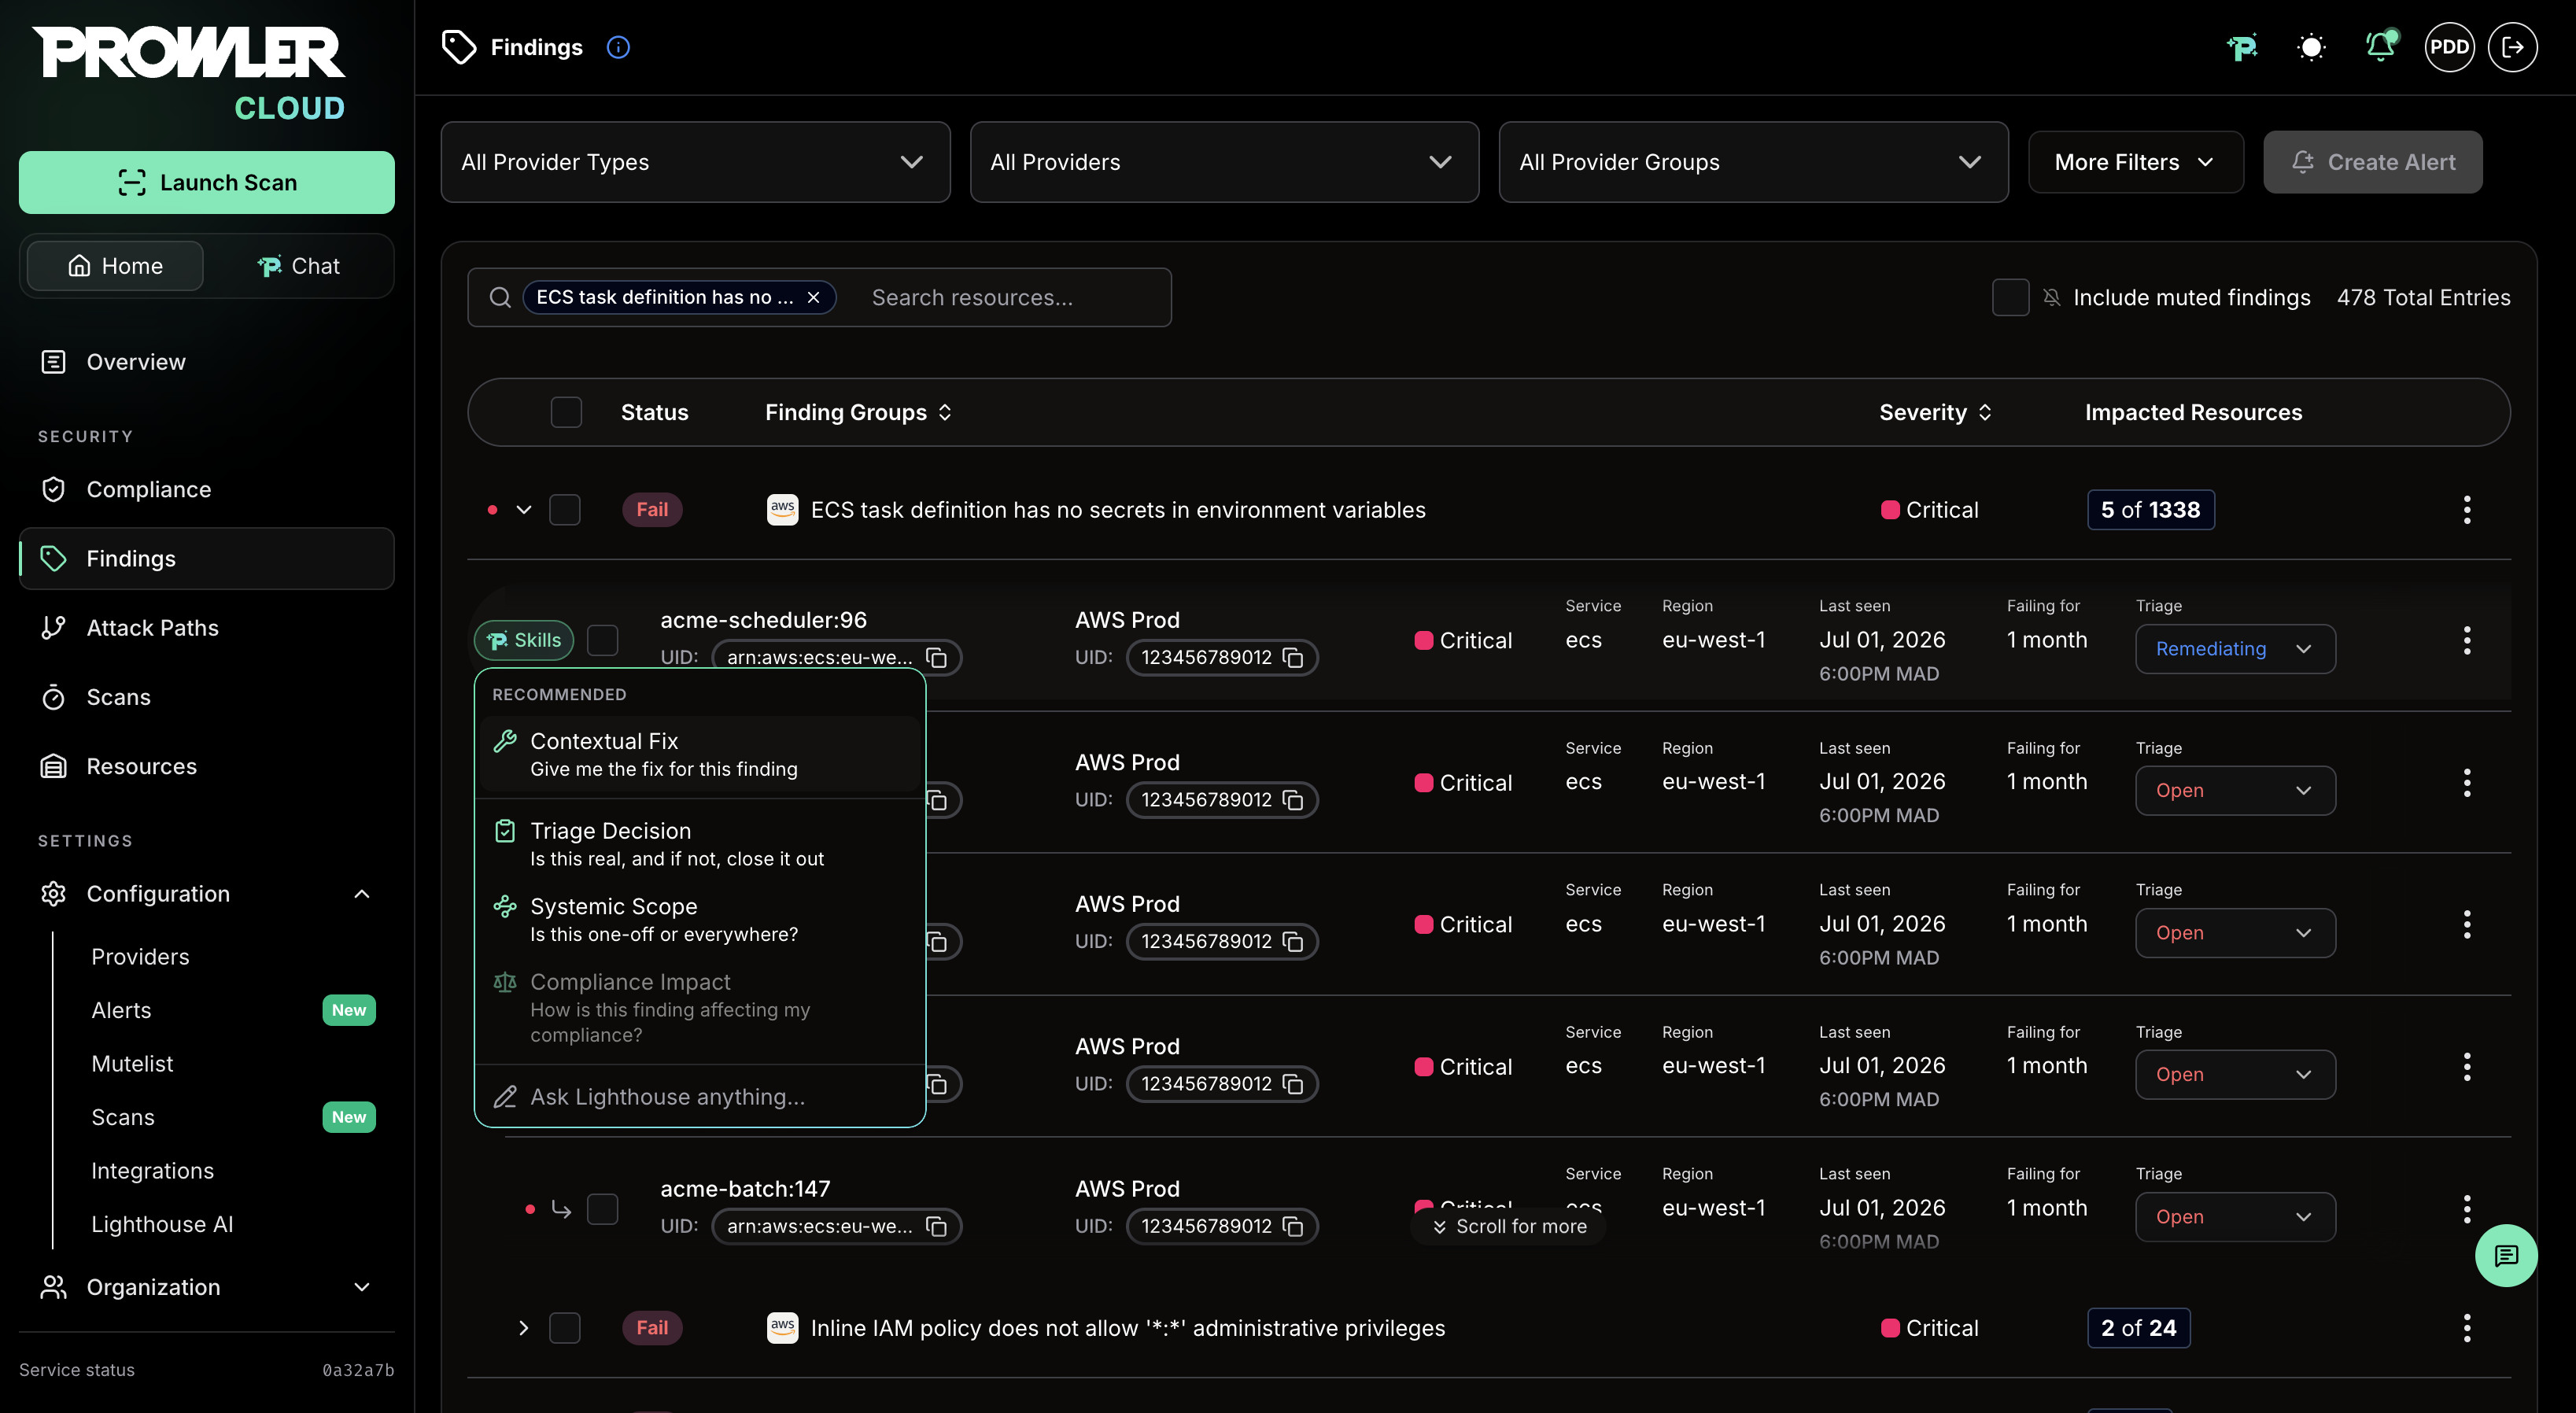
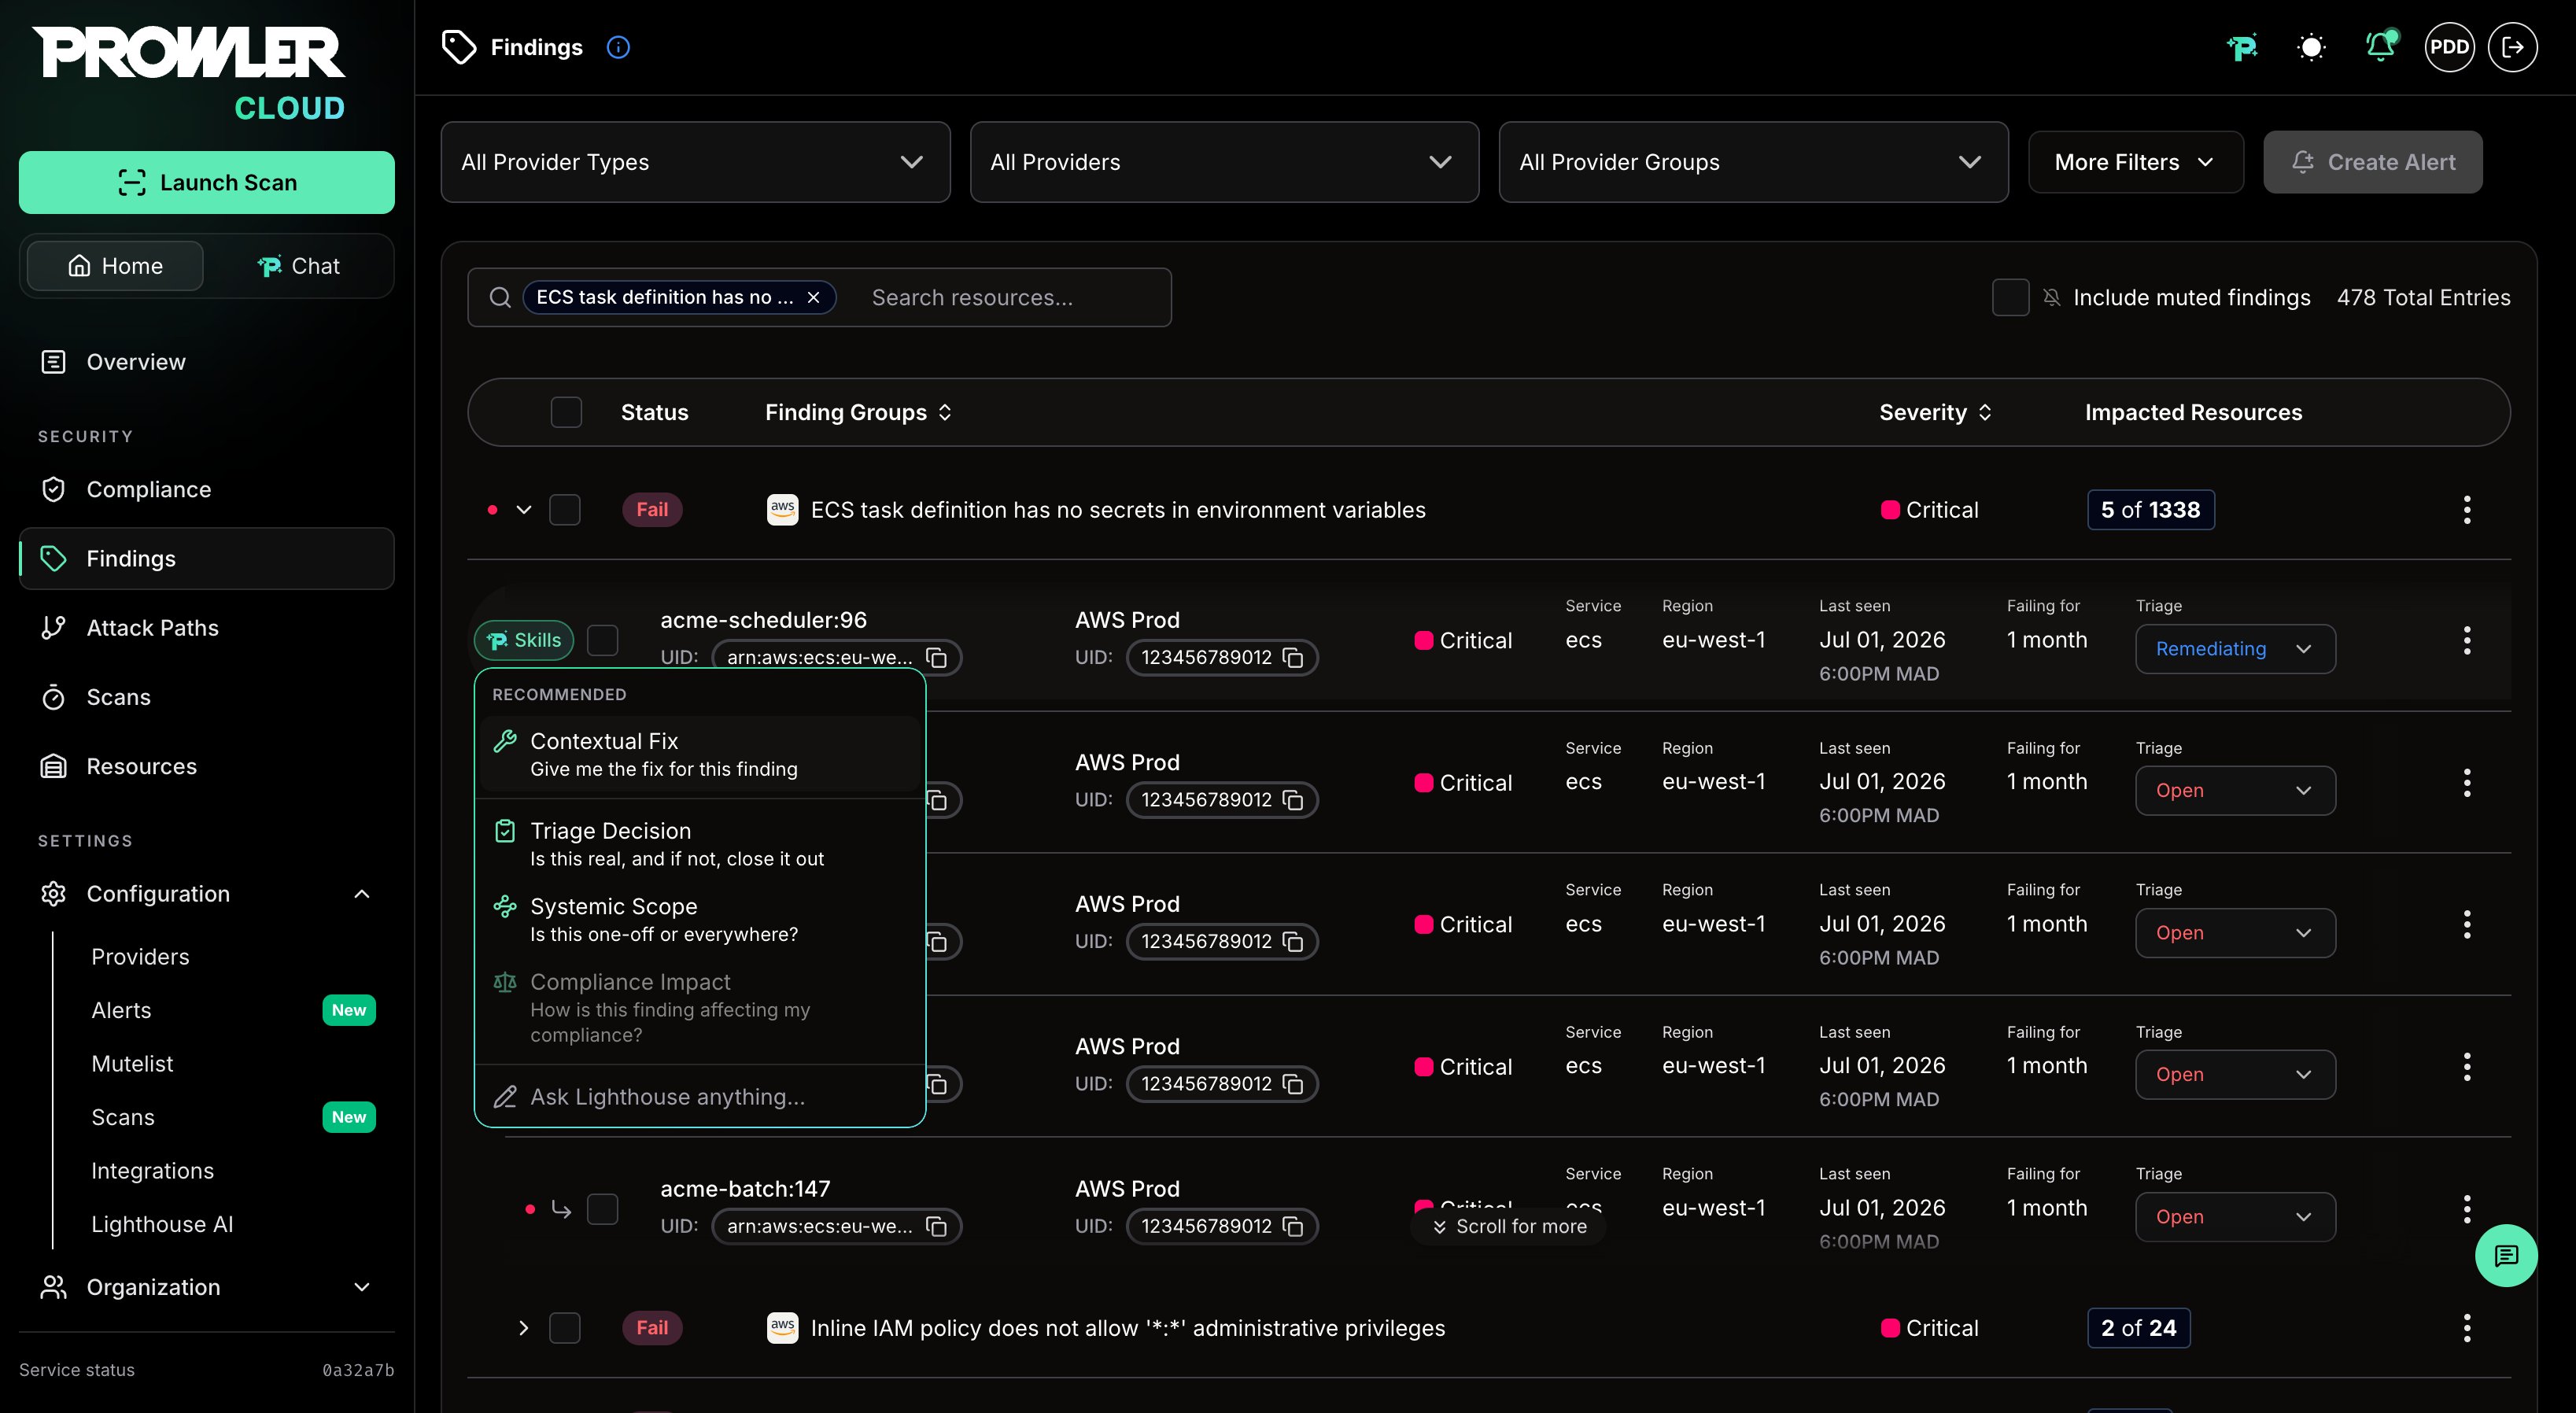
Adds Lighthouse AI Skills menu on every finding in Prowler Cloud, offering Contextual Fix, Triage Decision, Systemic Scope, and a free-form prompt, with follow-up actions including creating a Jira issue or muting the finding (Cloud/Private Cloud only).
5.39.0 · Aug 2026
· source
· release history
Adds Manage Lighthouse AI role permission in role forms and role details, allowing the Lighthouse AI configuration permission to be granted or restricted independently of other permissions (Cloud/Private Cloud only).
5.39.0 · Aug 2026
· source
· release history
Lighthouse AI (Prowler Cloud/Private Cloud) is now context-aware: messages carry the current page, open finding or resource, and its metadata, and Lighthouse can now invoke all MCP tool families (scan configurations, scheduling, finding triage, alert rules, integrations, users, and roles) subject to RBAC.
5.37.0 · Aug 2026
· source
· release history
docs
Context-Aware Chat The panel knows where you are in the app. Messages carry the page you are on and, when a finding or resource is open in the side panel, its metadata too, so questions like explain this resolve against what is on screen.
docs update · Aug 2026
· source
example
Configure Prowler Lighthouse with your preferred LLM and API key to enable natural-language security posture Q&A in the UI.$ In the console, go to the Lighthouse tab > Lighthouse Configuration Panel, select your LLM (e.g., GPT-4o Mini), enter your API Key, and optionally add business-specific context, then save.
5.8.0 · Jul 2025
· source
+Flexible check execution controlsverifiedProvides granular control over the scanning process through group-based filtering, exclusion of extra checks to improve performance, and standard output messaging.14 releases · 11 other sources · first seen Jan 2018▸
release
14 total
excluded_checks and excluded_services scan config options let you skip specific checks or entire services to reduce noise.
5.35.0 · Jul 2026
· source
· release history
AWS IAM customer-managed policy checks now scan only attached policies by default; opt in to auditing unattached policies with --scan-unused-services.
5.27.0 · May 2026
· source
· release history
New --excluded-checks-file CLI flag lets you supply a file of checks to exclude from a scan.
5.12.0 · Sep 2025
· source
· release history
Adds new --skip-api-check command-line flag for GCP provider scans.
5.11.0 · Aug 2025
· source
· release history
Adds new gen-ai check category to group and run checks for Generative AI, ML, and LLM services.
5.1.0 · Jan 2025
· source
· release history
ignore_unused_services boolean flag (default true) added to .prowler/config to exclude cloud provider service APIs that are not currently in use from scanning.
3.16.11 · Jul 2024
· source
· release history
command line
--aws-connect-timeout — Seconds to wait to establish a connection (TCP, proxy tunnel and TLS) to an AWS endpoint before retrying (Default: 10)
5.42.0 · Sep 2026
· command-line history
example
10 total
Scan a GovCloud account from a host that reaches AWS only through VPC endpoints, cutting per-region timeout from ~4 minutes to ~10 seconds per unreachable service.$ prowler aws --region us-gov-west-1 --aws-connect-timeout 10 --aws-read-timeout 60 --aws-retries-max-attempts 0
5.42.0 · Sep 2026
· source
Run only the new EKS deletion protection check to quickly audit clusters for missing safeguards.$ prowler aws --checks eks_cluster_deletion_protection_enabled
5.11.0 · Aug 2025
· source
Skip GCP API availability pre-checks to speed up scans in environments where APIs are known to be enabled.$ prowler gcp --skip-api-check
5.11.0 · Aug 2025
· source
List all available Microsoft365 checks before running a full assessment to understand coverage.$ prowler microsoft365 --list-checks
5.3.0 · Feb 2025
· source
Generate a quick inventory of AWS resources and save it to a specific CSV file for further analysis.$ prowler aws -i -F custom-output-file.csv
3.13.0 · Feb 2024
· source
Scan AWS and skip findings for services like S3 or Lambda that aren't actually deployed to reduce noise.$ prowler aws --ignore-unused-services
3.11.0 · Oct 2023
· source
+GCP cloud security checksshippedChecks GCP Cloud SQL high availability, Cloud Functions VPC and public access exposure, and Secret Manager public access and rotation settings.18 releases · 4 other sources · first seen Apr 2023▸
release
18 total
Adds a new GCP vertexai service with five Workbench checks — vertexai_workbench_instance_public_ip_disabled, vertexai_workbench_instance_root_access_disabled, vertexai_workbench_instance_terminal_access_disabled, vertexai_workbench_instance_file_download_disabled, and…
5.46.0 · Oct 2026
· source
· release history
GCP Organization onboarding in Prowler Cloud is now a single guided flow: provide an org-level credential, select folders and projects from a hierarchy tree, set aliases, test the connection, and register each project as a provider.
5.37.0 · Aug 2026
· source
· release history
New GCP checks: cloudsql_instance_high_availability_enabled, cloudfunction_function_inside_vpc, cloudfunction_function_not_publicly_accessible, secretmanager_secret_not_publicly_accessible, and secretmanager_secret_rotation_enabled.
5.31.0 · Jun 2026
· source
· release history
New GCP checks: cloudsql_instance_high_availability_enabled, cloudfunction_function_inside_vpc, cloudfunction_function_not_publicly_accessible, secretmanager_secret_not_publicly_accessible, and secretmanager_secret_rotation_enabled.
5.31.0 · Jun 2026
· source
· release history
Adds new GCP check cloudsql_instance_cmek_encryption_enabled to verify Cloud SQL instances use customer-managed encryption keys.
5.28.0 · May 2026
· source
· release history
Two new GCP checks for Gemini API coverage: apikeys_api_restricted_with_gemini_api and gemini_api_disabled.
5.23.0 · Apr 2026
· source
· release history
example
Detect unused GCP service accounts to identify dormant identities and reduce attack surface.$ prowler gcp --check iam_service_account_unused
5.6.0 · May 2025
· source
List all GCP projects accessible to the current credentials to verify scope before a full scan.$ prowler gcp --list-project-ids
4.1.0 · Apr 2024
· source
Run a CIS 2.0 compliant GCP scan, benefiting from the new 10x performance improvement.$ prowler gcp --compliance cis_2.0_gcp
3.8.0 · Aug 2023
· source
Assess a GCP project$ prowler gcp
+Azure cloud security checksshippedChecks Azure services including Cosmos DB, MySQL/PostgreSQL Flexible Servers, AKS, Databricks, and Defender CSPM for misconfigurations across resilience, access control, encryption, and monitoring.19 releases · 2 other sources · first seen Dec 2022▸
release
19 total
Improves Azure App Service runtime checks: raises the default php_latest_version for app_ensure_php_version_is_latest from 8.2 to 8.5 in both the SDK and the Prowler App scan configuration template, and makes app_ensure_php_version_is_latest, app_ensure_python_version_is_latest, and…
5.46.0 · Oct 2026
· source
· release history
Uses cloud-specific endpoints for Azure Defender and Key Vault based on --azure-region flag instead of hardcoded hosts
5.43.0 · Sep 2026
· source
· release history
New Azure check app_function_ensure_http_is_redirected_to_https: verifies that Function Apps enforce HTTPS-only traffic.
5.34.0 · Jul 2026
· source
· release history
New Azure check app_function_ensure_http_is_redirected_to_https: verifies that Function Apps enforce HTTPS-only traffic.
5.34.0 · Jul 2026
· source
· release history
New Azure checks across Cosmos DB (automatic failover, continuous backup, TLS 1.2, public access disabled), MySQL/PostgreSQL Flexible Servers (geo-redundant backup, HA), AKS (auto-upgrade, Container Insights, local accounts disabled, Defender), Databricks (public access, secure connectivity), Defender CSPM Standard…
5.31.0 · Jun 2026
· source
· release history
New Azure checks spanning Cosmos DB (automatic failover, continuous backup, TLS 1.2, public access), MySQL/PostgreSQL Flexible Servers (geo-redundant backup, high availability), AKS (auto-upgrade, Container Insights, local accounts disabled, Defender), Databricks (public network access, secure cluster connectivity),…
5.31.0 · Jun 2026
· source
· release history
example
Run Azure security checks against the latest CIS Benchmark v2.1 standard$ prowler azure --compliance cis_2.1_azure
3.16.0 · Apr 2024
· source
Assess an Azure subscription$ prowler azure --subscription <id>
+DORA compliance frameworkshippedMaps DORA requirements across AWS, Azure, GCP, Cloudflare, and Alibaba Cloud, with export in OCSF Compliance Finding format for SIEM ingestion.17 releases · 4 other sources · first seen Feb 2025▸
release
17 total
Adds CMMC 2.0 as a universal compliance framework covering all 149 requirements across Levels 1, 2, and 3, mapped to checks across AWS, Azure, GCP, Alibaba Cloud, Oracle Cloud, and Microsoft 365.
5.39.0 · Aug 2026
· source
· release history
Compliance view in Prowler Cloud now groups frameworks across all providers of the same type, rolling up into a consolidated posture with per-provider breakdown, findings drill-down, and combined executive PDF report; tabs are renamed to Single Scan and Multiple Scans, with Multiple Scans as the new default.
5.37.0 · Aug 2026
· source
· release history
New Cross-Provider Compliance view (Prowler Cloud/Private Cloud): rolls up the most recent scan of every compatible provider into a single compliance posture per framework (CIS Controls 8.1, CSA CCM 4.0, DORA 2022/2554) with per-provider breakdown and combined executive PDF export.
5.34.0 · Jul 2026
· source
· release history
Extends DORA (EU 2022/2554) compliance framework coverage to Azure, GCP, Cloudflare, and Alibaba Cloud under the DORA_2022_2554 framework identifier.
5.31.0 · Jun 2026
· source
· release history
Adds DORA (2022/2554) compliance framework mapping to Azure, GCP, Cloudflare, and Alibaba Cloud providers (use framework name DORA_2022_2554).
5.31.0 · Jun 2026
· source
· release history
UI adds dedicated compliance detail pages and icons for DISA Okta IDaaS STIG V1R2 and DORA frameworks.
5.30.0 · Jun 2026
· source
· release history
example
Assess your AWS environment against the DORA regulation framework to report on all five resilience pillars.$ prowler aws --compliance DORA_2022_2554
5.31.0 · Jun 2026
· source
Score your Microsoft 365 tenant's security posture with Prowler ThreatScore to quickly prioritize the highest-risk misconfigurations.$ prowler m365 --compliance prowler_threatscore_m365
5.7.0 · May 2025
· source
Enumerate all new M365 checks across Teams, Defender, Purview, and Exchange before running a full assessment.$ prowler m365 --services teams defender purview exchange --list-checks
5.6.0 · May 2025
· source
Audit a Microsoft365 tenant using a registered Entra app (service principal) — useful for automated pipelines where interactive login is unavailable.$ prowler microsoft365 --sp-env-auth
5.3.0 · Feb 2025
· source
+Cloud provider scanning expansionshippedAdds security checks for Alibaba Cloud OSS versioning, Okta Bedrock guardrails, IAM Roles Anywhere permission scoping, GCP Workload Identity Federation attribute conditions, AWS Inspector2 coverage and KEV tracking, GitHub Actions default permissions, and Microsoft 365 domain DMARC enforcement.18 releases · 1 other source · first seen Jan 2026▸
release
18 total
Adds seven new AWS checks: inspector2_coverage_scan_status_active, inspector2_coverage_recently_scanned (configurable via inspector2_max_days_since_last_scan, default 3), inspector2_active_findings_no_known_exploited_vulnerabilities, inspector2_active_findings_kev_within_due_date,…
5.43.0 · Sep 2026
· source
· release history
Adds UI_SELF_REGISTRATION_ENABLED environment variable for Prowler Private Cloud deployments; set to false to make sign-up invitation-only, hiding the Sign up link and Create organization option.
5.43.0 · Sep 2026
· source
· release history
Adds seven new AWS Inspector checks including inspector2_active_findings_kev_within_due_date and elbv2_listener_fips_tls_enabled
5.43.0 · Sep 2026
· source
· release history
Adds AWS partition bootstrap failover: when PROWLER_AWS_PARTITION is set, bootstrap STS calls try up to two additional regions in the partition on connection errors or timeouts, so GovCloud scans succeed on networks that route only to one regional endpoint.
5.43.0 · Sep 2026
· source
· release history
Adds inspector2:BatchGetFindingDetails to the Prowler additions policy and CloudFormation scan role so KEV checks can pull CISA Known Exploited Vulnerability data directly from Inspector without an external feed; missing permission reports MANUAL instead of a false FAIL.
5.43.0 · Sep 2026
· source
· release history
Adds support for AWS ISO partitions (aws-iso, aws-iso-b, aws-iso-e, aws-iso-f) in the service region matrix, so ISO regions such as us-isob-east-1 are accepted by --region and --excluded-region without a hand-edited aws_regions_by_service.json.
5.42.0 · Sep 2026
· source
· release history
example
Check AWS resources for active findings listed in the CISA Known Exploited Vulnerabilities catalog.$ prowler aws --checks inspector2_active_findings_kev_within_due_date
5.43.0 · Sep 2026
· source
+AWS Bedrock security checksshippedVerifies that AWS Bedrock Agents run with least-privilege IAM roles and that privilege-escalation checks extend to Bedrock AgentCore execution paths.16 releases · 1 other source · first seen Dec 2024▸
release
16 total
Adds bedrock_guardrail_sensitive_information_filter_enforced, which flags Bedrock guardrails whose PII entities or custom regexes take no action on the output path, and bedrock_model_invocation_logging_text_data_enabled, which verifies that model invocation logging delivers prompt and response text instead of only…
5.46.0 · Oct 2026
· source
· release history
Improves bedrock_api_key_no_long_term_credentials to report Bedrock long-term API keys that never expire (keys created without an expiration period were previously skipped and produced no finding).
5.46.0 · Oct 2026
· source
· release history
New check iam_policy_no_agentcore_workload_access_token_wildcard flags customer-managed IAM policies granting bedrock-agentcore:GetWorkloadAccessToken, GetWorkloadAccessTokenForJWT, or GetWorkloadAccessTokenForUserId on resources reaching workload identities beyond the caller's own.
5.41.0 · Sep 2026
· source
· release history
New check iam_policy_passrole_to_bedrock_agentcore_restricted flags customer-managed IAM policies that allow iam:PassRole over every role where the passed role can reach Bedrock AgentCore.
5.41.0 · Sep 2026
· source
· release history
Adds ten new AWS checks: iam_policy_passrole_to_bedrock_agentcore_restricted, iam_policy_no_agentcore_workload_access_token_wildcard, cloudwatch_log_group_agentcore_data_protection_policy_enabled, guardduty_runtime_monitoring_enabled, guardduty_ai_protection_enabled, ecr_registry_enhanced_scanning_enabled,…
5.41.0 · Sep 2026
· source
· release history
Configures Bedrock AgentCore log group data protection check using the agentcore_log_group_name_prefixes key in config.yaml
5.41.0 · Sep 2026
· source
· release history
example
Audit your AWS Bedrock deployment for missing Guardrails, unversioned prompts, and unencrypted prompt storage in one pass.$ prowler aws --checks bedrock_guardrails_configured bedrock_prompt_management_exists bedrock_prompt_encrypted_with_cmk
5.26.0 · May 2026
· source
+Selective resource scanningshippedAllows limiting scans to specific resources via ARNs, tags, or projects to reduce scope and improve performance.9 releases · 8 other sources · first seen Feb 2023▸
Also counts toward: Command-line interface
release
9 total
New --resource-group and --list-resource-groups CLI flags to filter checks by resource group across all providers.
5.23.0 · Apr 2026
· source
· release history
Adds --repository and --organization CLI flags for scoped GitHub scanning, letting you target specific repos or orgs instead of scanning everything.
5.10.0 · Aug 2025
· source
· release history
Adds new --organization-id flag for GCP scans to limit scope to projects within a specific Google Cloud organization.
4.5.0 · Nov 2024
· source
· release history
The --project-ids flag for the GCP provider now accepts * as a prefix or suffix to filter project IDs.
4.1.0 · Apr 2024
· source
· release history
Adds the --excluded-project-ids flag to exclude specific projects from scanning, also supporting * wildcards.
4.1.0 · Apr 2024
· source
· release history
--scan-unused-services flag to include unused AWS services in execution
4.0.0 · Apr 2024
· source
· release history
example
8 total
Run only the new Vertex AI Workbench checks against a GCP project to identify publicly reachable or over-privileged notebook instances.$ prowler gcp --checks vertexai_workbench_instance_public_ip_disabled vertexai_workbench_instance_root_access_disabled vertexai_workbench_instance_terminal_access_disabled…
5.46.0 · Oct 2026
· source
Scope the AgentCore log-group data-protection check to your organization's specific log group prefixes.$ agentcore_log_group_name_prefixes: - "/aws/bedrock/agentcore/prod-" - "/aws/bedrock/agentcore/staging-"
5.41.0 · Sep 2026
· source
List all resource groups available across providers, then scope a scan to a specific resource group to reduce noise.$ prowler aws --list-resource-groups prowler aws --resource-group <resource_group_name>
5.23.0 · Apr 2026
· source
Limit a GitHub scan to one or more organizations to reduce noise in large multi-org environments.$ prowler github --organization acme-org other-org
5.10.0 · Aug 2025
· source
Scan only specific repositories in a GitHub org to quickly audit a subset of your codebase.$ prowler github --repository acme/app acme/lib
5.10.0 · Aug 2025
· source
Scope a GCP scan to only projects within a specific organization to avoid scanning unrelated projects.$ prowler gcp --organization-id <organization-id>
4.5.0 · Nov 2024
· source
+Attack Paths analysisshippedExecutes graph-based queries and visualizes attack vectors to identify privilege escalation and lateral movement paths across AWS environments using Cartography and Neo4j.14 releases · 2 other sources · first seen Jan 2026▸
Also counts toward: REST API, Scripting API
release
14 total
Attack Paths query catalog exposes an outcome metadata field (Code execution, Privilege escalation, Public exposure, Resource inventory)
5.38.0 · Aug 2026
· source
· release history
Attack Paths graph in the Prowler App rewritten on React Flow with improved layout, pan/zoom, image export, and a minimap.
5.27.0 · May 2026
· source
· release history
Neo4j connection_acquisition_timeout for Attack Paths is now configurable via the NEO4J_CONN_ACQUISITION_TIMEOUT env var.
5.24.4 · Apr 2026
· source
· release history
Attack Paths View Finding now opens the finding drawer inline over the graph, preserving graph zoom, selection, and filter state.
5.24.0 · Apr 2026
· source
· release history
Attack Paths custom query editor now includes syntax highlighting and line numbering for openCypher queries.
5.23.0 · Apr 2026
· source
· release history
Adds custom openCypher query support in Attack Paths, with Cartography schema guidance and Lighthouse AI assistance for query generation.
5.22.0 · Mar 2026
· source
· release history
example
Raise the Neo4j connection acquisition timeout if your Attack Paths graph queries are timing out after the new 15 s default.$ NEO4J_CONN_ACQUISITION_TIMEOUT=60 <your API start command>
5.24.4 · Apr 2026
· source
Explore lateral movement paths or custom threat scenarios in your cloud graph without being limited to predefined queries.$ In the Prowler Cloud UI, go to Attack Paths, open the query panel, select 'Custom Query', enter your openCypher query (optionally use Lighthouse AI to generate it), and click Run.
5.22.0 · Mar 2026
· source
+Cloud resource scanning expansionshippedAdds new security checks for Azure Container Registries, AWS CloudFront, Lambda, ECS, EC2, IAM, and AWS Organizations services.12 releases · 3 other sources · first seen Sep 2024▸
release
12 total
Adds AWS checks batch_job_definition_no_secrets to detect secrets in Batch job environment variables and awslambda_layer_no_secrets_in_content to scan Lambda layer package content
5.39.0 · Aug 2026
· source
· release history
New AWS check iam_user_access_not_stale_to_sagemaker flags IAM users with SageMaker access exceeding 90 days (tunable via max_unused_sagemaker_access_days) or who have never accessed SageMaker.
5.27.0 · May 2026
· source
· release history
New iam_role_access_not_stale_to_bedrock and iam_user_access_not_stale_to_bedrock checks detect dormant GenAI access that hasn't been used recently.
5.24.0 · Apr 2026
· source
· release history
New AWS check ec2_securitygroup_allow_ingress_from_internet_to_any_port_from_ip using ipaddress.is_global for accurate public IP detection.
5.23.0 · Apr 2026
· source
· release history
New AWS checks awslambda_function_no_dead_letter_queue, awslambda_function_using_cross_account_layers, and awslambda_function_env_vars_not_encrypted_with_cmk.
5.23.0 · Apr 2026
· source
· release history
Adds new check ec2_instance_with_outdated_ami for AWS.
5.13.0 · Oct 2025
· source
· release history
example
Include unattached customer-managed IAM policies in your AWS scan (previously the default behaviour) alongside other unused-service surfaces.$ prowler aws --scan-unused-services
5.27.0 · May 2026
· source
Verify that AWS Organizations centralized root credentials management is enabled across your account.$ prowler aws -c iam_root_credentials_management_enabled
4.6.0 · Nov 2024
· source
Audit Azure Container Registries to confirm the admin user account is disabled across your subscription.$ prowler azure -c containerregistry_admin_user_disabled
4.4.0 · Sep 2024
· source
+Provider Group filtering in Prowler CloudshippedScopes the Prowler Cloud Overview, Findings, Resources, Scans, and Providers views to a selected team or environment group in a single click.11 releases · 1 other source · first seen Mar 2025▸
release
11 total
Restricts GET /resources/metadata, GET /resources/metadata/latest, GET /findings/metadata, and GET /findings/metadata/latest to honour the provider groups of the caller role instead of aggregating every provider in the tenant.
5.46.0 · Oct 2026
· source
· release history
Prowler Cloud/Enterprise: Provider Group Filter scopes the Overview, Findings, Resources, Scans, and Providers views to a team or environment in a single click.
5.32.0 · Jul 2026
· source
· release history
Adds provider group filter across Overview, Findings, Resources, Scans, and Providers views in Prowler Cloud/Enterprise to scope the whole app to a team, environment, or business unit.
5.32.0 · Jul 2026
· source
· release history
Account and provider-type selector triggers now display the provider icon with a non-deduped icon stack for easier visual identification.
5.29.2 · Jun 2026
· source
· release history
New group filter on GET /findings and GET /findings/metadata/latest endpoints for resource-group-based finding queries.
5.17.0 · Jan 2026
· source
· release history
Adds provider-type filters and optional pagination disable to GET /api/v1/providers.
5.14.0 · Nov 2025
· source
· release history
example
Scope findings metadata API calls to only the provider groups the caller role can see, confirming the new per-role scoping is in effect.$ curl -s -H 'Authorization: Bearer <token>' 'https://<prowler-api>/api/v1/resources/metadata/latest'
5.46.0 · Oct 2026
· source
+AWS Boto3 retry configurationshippedExposes an environment variable to control the number of Boto3 retry attempts for AWS provider calls, including setting it to zero to disable retries entirely in environments with slow or unreachable endpoints.10 releases · 2 other sources · first seen Sep 2026▸
release
10 total
Adds PROWLER_AWS_BOTO3_RETRIES_MAX_ATTEMPTS environment variable to control Boto3 retry attempts for the AWS provider; set to 0 to disable retries entirely.
5.44.0 · Sep 2026
· source
· release history
Adds PROWLER_AWS_BOTO3_RETRIES_MAX_ATTEMPTS environment variable to control Boto3 retry attempts for deployments building the AWS provider without CLI flags; set to 0 to disable retries.
5.44.0 · Sep 2026
· source
· release history
Adds AWS partition bootstrap failover: when PROWLER_AWS_PARTITION is set, bootstrap STS calls try up to two additional regions in the partition on connection errors or timeouts, so GovCloud scans succeed on networks that route only to one regional endpoint.
5.43.0 · Sep 2026
· source
· release history
Adds --aws-connect-timeout and --aws-read-timeout CLI flags, plus PROWLER_AWS_BOTO3_CONNECT_TIMEOUT and PROWLER_AWS_BOTO3_READ_TIMEOUT environment variables, to control per-call AWS API wait times; --aws-retries-max-attempts 0 now disables Boto3 retries entirely instead of silently falling back to three…
5.42.0 · Sep 2026
· source
· release history
Adds support for AWS ISO partitions (aws-iso, aws-iso-b, aws-iso-e, aws-iso-f) in the service region matrix, so ISO regions such as us-isob-east-1 are accepted by --region and --excluded-region without a hand-edited aws_regions_by_service.json.
5.42.0 · Sep 2026
· source
· release history
Lowers the default Boto3 connect timeout from 60 seconds to 10 seconds, cutting scan time in restricted-egress networks (VPC endpoints, GovCloud, private deployments) where unreachable service endpoints previously cost up to four 60-second attempts per region.
5.42.0 · Sep 2026
· source
· release history
example
Cap Boto3 retries for AWS provider calls in an environment where some AWS endpoints are slow or unreachable.$ PROWLER_AWS_BOTO3_RETRIES_MAX_ATTEMPTS=3
5.44.0 · Sep 2026
· source
Cap Boto3 retries for the AWS provider in environments where unreachable partition endpoints cause long delays during connection tests.$ PROWLER_AWS_BOTO3_RETRIES_MAX_ATTEMPTS=3
5.44.0 · Sep 2026
· source
+External provider and compliance framework extensibilityshippedAllows discovery and use of custom providers, checks, and compliance frameworks — including universal ones — without modifying core Prowler code.11 releases · 1 other source · first seen Apr 2022▸
Also counts toward: Plugin API support, Plugin system
release
11 total
Adds registry marketplace and external provider onboarding for Private Cloud, with permission-based access, schema-driven credentials, connection checks, and scan launch.
5.43.0 · Sep 2026
· source
· release history
Surfaces pre-configured credential creation links in the add-provider wizard: Cloudflare exposes a User API Token template and an Account-Owned template pinned to the entered Cloudflare Account ID; GitHub exposes a personal-repositories template and an organization-scanning template pinned to the entered identifier.
5.39.0 · Aug 2026
· source
· release history
Enables dynamic providers to be renamed and deleted directly from the Providers table.
5.35.0 · Jul 2026
· source
· release history
Dynamically registered (custom) providers are now listed, filtered, and rendered across the UI with a generic icon, humanized label, and Custom badge.
5.34.0 · Jul 2026
· source
· release history
UI now lists, filters, and renders dynamically registered (custom) providers with a generic icon, humanized label, and Custom badge when no bespoke assets exist.
5.34.0 · Jul 2026
· source
· release history
Adds support for external/custom providers, checks, and compliance frameworks without modifying Prowler core code.
5.30.0 · Jun 2026
· source
· release history
example
Run Prowler with custom checks and allowlists stored in an S3 bucket.$ prowler -w s3://bucket/prefix/allowlist_sample.txt
2.9.0 · Apr 2022
· source
+Compliance PDF report generationshippedGenerates compliance PDF reports from provider metadata stored in the database without requiring active provider credentials at report time.10 releases · 1 other source · first seen Apr 2021▸
release
10 total
Compliance PDF reports now generate without active provider credentials, drawing on provider metadata stored in the database.
5.33.0 · Jul 2026
· source
· release history
Compliance PDF reports now generate without requiring provider credentials, drawing findings from provider metadata stored in the database.
5.33.0 · Jul 2026
· source
· release history
PDF Compliance Reports now include only failed findings and cap per-check detail tables at 100 failed findings with a banner pointing to CSV/JSON exports.
5.27.0 · May 2026
· source
· release history
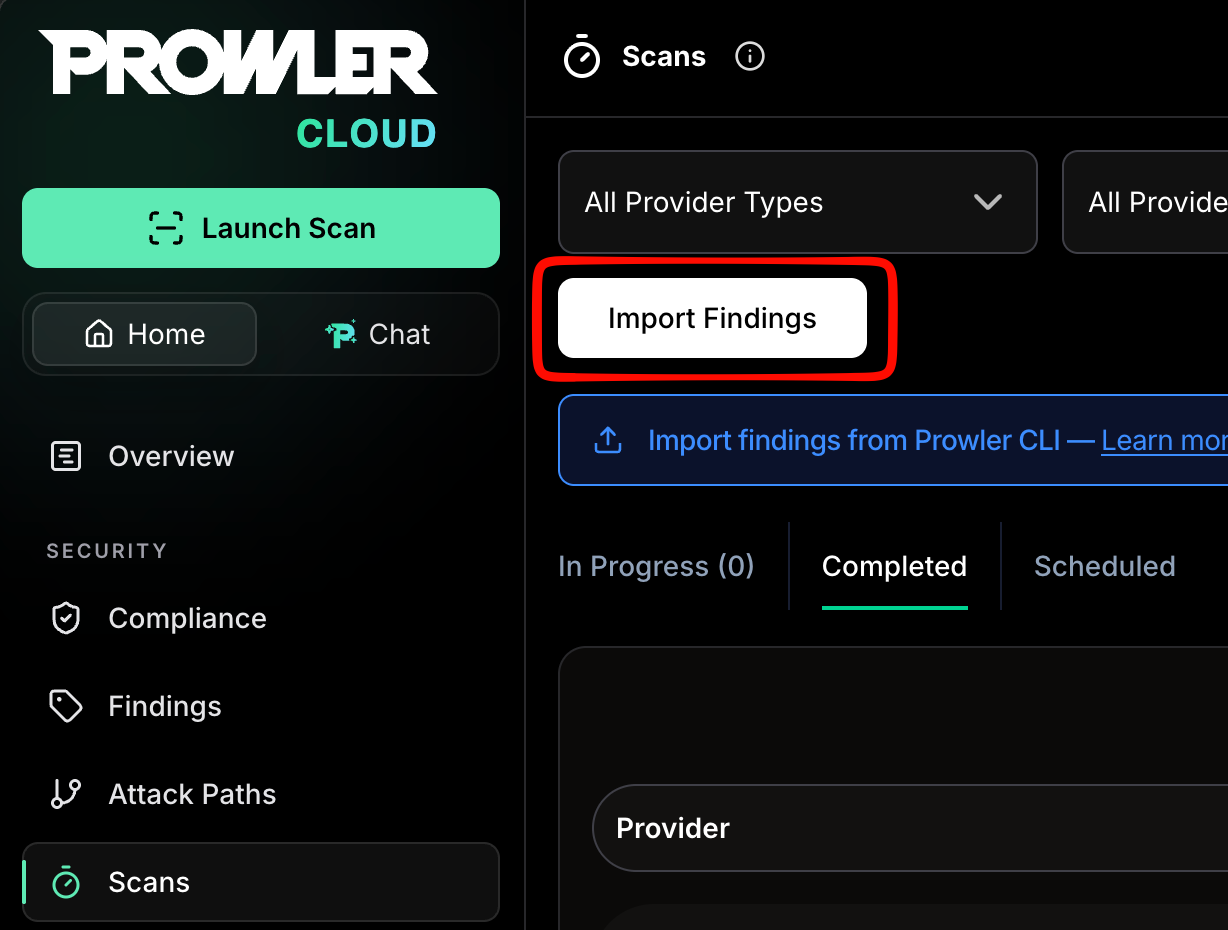
Imported OCSF scans in Prowler Cloud now generate the same downloadable report artifacts as CLI scans.
5.25.0 · Apr 2026
· source
· release history
PDF reports now include Account ID, Alias, and Provider Name directly in the reporting table.
5.16.0 · Dec 2025
· source
· release history
Adds PDF reporting for ENS, NIS2, and Prowler ThreatScore compliance frameworks.
5.14.0 · Nov 2025
· source
· release history
example
Send Prowler findings to AWS Security Hub for centralized compliance tracking.$ prowler -M ashf
2.4.0 · Apr 2021
· source
+Finding whitelisting and suppressionshippedAllows users to suppress or whitelist specific findings by providing a file with regex patterns for flexible matching.10 releases · 1 other source · first seen Apr 2021▸
Also counts toward: Command-line interface
release
10 total
Introduces Simple Mutelist: mute findings directly from the findings table and manage mute rules via a new /mutelist page with Simple and Advanced (YAML) tabs.
5.16.0 · Dec 2025
· source
· release history
Adds muting of findings based on simple rules with a custom reason via the API.
5.14.0 · Nov 2025
· source
· release history
Adds a Mutelist shortcut under the UI Configuration section menu.
5.11.0 · Aug 2025
· source
· release history
Adds default Mutelist placeholder in the UI.
5.10.0 · Aug 2025
· source
· release history
New /processors API endpoint enables post-processing of findings; currently supports the Mutelist processor for muting findings programmatically.
5.9.0 · Jul 2025
· source
· release history
Adds resource_tag filter support to the findings API endpoint.
5.1.3 · Jan 2025
· source
· release history
example
Whitelist findings using a file that supports regex patterns for flexible matching.$ prowler -w my_whitelist.yml
2.4.0 · Apr 2021
· source
+AWS org-wide governance checksshippedChecks that AWS Security Hub and Config delegated admin with org-wide aggregation are enabled across all regions.8 releases · 2 other sources · first seen Feb 2020▸
release
8 total
Providers table now shows an Imported provider indicator for providers whose findings were uploaded via the Prowler CLI, distinguishing them from connected providers at a glance.
5.40.0 · Aug 2026
· source
· release history
Adds one-step AWS Organizations onboarding: a single CloudFormation quick-create link deploys the management account role and a service-managed StackSet to every member account (Prowler Cloud/Private Cloud).
5.35.0 · Jul 2026
· source
· release history
New AWS check ec2_ami_account_block_public_access: verifies AMI block public access is enabled at the account level per region.
5.34.0 · Jul 2026
· source
· release history
New AWS org-wide governance checks: securityhub_delegated_admin_enabled_all_regions and config_delegated_admin_and_org_aggregator_all_regions.
5.31.0 · Jun 2026
· source
· release history
New AWS organization-wide governance checks: securityhub_delegated_admin_enabled_all_regions and config_delegated_admin_and_org_aggregator_all_regions.
5.31.0 · Jun 2026
· source
· release history
Adds two new AWS check categories: privilege-escalation and ec2-imdsv1, improving visibility into high-risk misconfigurations.
5.16.0 · Dec 2025
· source
· release history
example
Verify GuardDuty delegated admin is configured in every region as part of a multi-account security baseline audit.$ prowler aws --check guardduty_delegated_admin_enabled_all_regions
5.20.0 · Mar 2026
· source
Suppress all passing checks and only display failures for faster CI feedback.$ prowler -q
2.2.0 · Feb 2020
· source
+GitHub repository ruleset checksshippedEvaluates GitHub branch-protection status against both legacy branch protection rules and the newer repository rulesets.8 releases · 1 other source · first seen Jul 2025▸
release
8 total
Adds GitHub organization action pull request approval disabled check organization_actions_pull_request_approval_disabled
5.40.0 · Aug 2026
· source
· release history
Scales organization_repository_creation_limited GitHub check severity to low when repository creation is limited to private or internal visibility.
5.39.0 · Aug 2026
· source
· release history
GitHub branch-protection checks now evaluate repository rulesets in addition to branch protection rules.
5.32.0 · Jul 2026
· source
· release history
Adds organization_repository_deletion_limited check for GitHub: verifies that organization repository deletion and transfer is restricted to owners.
5.21.0 · Mar 2026
· source
· release history
New GitHub check repository_immutable_releases_enabled detects repositories without immutable releases enforced.
5.15.0 · Dec 2025
· source
· release history
Adds new GitHub check organization_default_repository_permission_strict.
5.14.0 · Nov 2025
· source
· release history
example
Combine repository and organization scoping for a tightly targeted GitHub security assessment.$ prowler github --organization acme-org --repository acme/app acme/lib
5.10.0 · Aug 2025
· source
+Google Workspace provider scanningshippedCovers Gmail, Chat, Sites, and other Google Workspace services with checks for attachment safety, spoofing protection, and external sharing controls.8 releases · first seen Mar 2026▸
release
8 total
Improves Google Workspace checks and findings: findings now state when a feature is not available on the tenant edition (e.g.
5.46.0 · Oct 2026
· source
· release history
Adds four new Google Workspace services with six new checks — Sites (sites_service_disabled), Additional Services (additionalservices_external_groups_disabled), Marketplace (marketplace_apps_access_restricted), and Groups (groups_creation_restricted, groups_external_access_restricted,…
5.28.0 · May 2026
· source
· release history
Google Workspace gains a Chat service with 6 CIS-mapped checks covering app installation, external file sharing, external messaging, external spaces, incoming webhooks, and internal file sharing.
5.27.0 · May 2026
· source
· release history
Adds eight new Google Workspace Gmail checks covering attachment safety (gmail_anomalous_attachment_protection_enabled, gmail_encrypted_attachment_protection_enabled, gmail_script_attachment_protection_enabled) and spoofing protection (gmail_domain_spoofing_protection_enabled,…
5.26.0 · May 2026
· source
· release history
New Google Workspace Gmail service with 9 CIS-aligned checks covering mail delegation, link scanning, POP/IMAP access, auto-forwarding, and more.
5.25.0 · Apr 2026
· source
· release history
Adds Google Workspace provider full support in the Prowler App UI — connect and scan Google Workspace environments directly from the interface.
5.21.0 · Mar 2026
· source
· release history
+AWS Organizations one-step onboardingshippedDeploys a management role and a service-managed StackSet to every AWS member account via a single CloudFormation quick-create link.8 releases · first seen Jan 2025▸
release
8 total
Adds a one-step Add Provider wizard for AWS accounts that reads the account ID from the role ARN and handles credentials and connection testing in a single submit.
5.44.0 · Sep 2026
· source
· release history
Connects AWS accounts in a single wizard step: the account ID is read from the role ARN (or typed for static access keys), the role is assumed, and credentials are stored and tested in one submit.
5.44.0 · Sep 2026
· source
· release history
Adds one-step AWS Organizations onboarding: a single CloudFormation quick-create link deploys the management account role and a service-managed StackSet to every member account (Prowler Cloud/Private Cloud).
5.35.0 · Jul 2026
· source
· release history
One-step AWS Organizations onboarding uses a single CloudFormation quick-create link to deploy management and member roles.
5.35.0 · Jul 2026
· source
· release history
AWS Organizations onboarding in Prowler Cloud allows connecting multiple AWS accounts from an Organization hierarchy in a single flow.
5.19.0 · Mar 2026
· source
· release history
Unified provider connection wizard redesigned as a modal with a consistent experience across all provider types.
5.19.0 · Mar 2026
· source
· release history
+Huawei Cloud provider scanningverifiedScans Huawei Cloud accounts for misconfigurations across CTS, ECS, ELB, IAM, KMS, OBS, RDS, VPC, WAF, and other services.4 releases · 4 other sources · first seen Aug 2026▸
release
Adds smn_topic_subscriptions check for Huawei Cloud, reporting SMN topics that have no subscriptions configured.
5.43.0 · Sep 2026
· source
· release history
New vpc_security_group_open_egress check (Huawei Cloud) flags VPC security groups that allow open egress to the internet.
5.40.0 · Aug 2026
· source
· release history
Adds HUAWEICLOUD_ACCESS_KEY_ID and HUAWEICLOUD_SECRET_ACCESS_KEY environment variables to authenticate a new huaweicloud provider, enabling prowler huaweicloud scans across 25 checks covering CTS, ECS, ELB, EVS, IAM, KMS, OBS, RDS, VPC, and WAF, plus the CIS Huawei Cloud Foundations Benchmark 1.0.
5.37.0 · Aug 2026
· source
· release history
Adds huaweicloud as a supported provider with 25 checks across CTS, ECS, ELB, EVS, IAM, KMS, OBS, RDS, VPC, and WAF services.
5.37.0 · Aug 2026
· source
· release history
docs
Prowler for Huawei Cloud scans your Huawei Cloud account for security misconfigurations across compute, storage, networking, identity, encryption, database, and logging services. Huawei Cloud support in Prowler is community-maintained. For commercial support or to request additional service coverage, contact us .
docs update · Aug 2026
· source
--cloud — Scan every region of a Huawei Cloud instance (international, europe, or china) without listing regions. Also selects the matching endpoint (.eu for europe, .com otherwise). Overridden by --region. Defaults to the HUAWEICLOUD_CLOUD environment variable.
5.37.0 · Aug 2026
· command-line history
example
Scan a Huawei Cloud account for the first time using IAM user access key credentials.$ export HUAWEICLOUD_ACCESS_KEY_ID="your-access-key-id" export HUAWEICLOUD_SECRET_ACCESS_KEY="your-secret-access-key" prowler huaweicloud
5.37.0 · Aug 2026
· source
+Attack Paths graph storageshippedStores attack path graphs in AWS Neptune or Neo4j, selectable via configuration, for cross-provider graph-based attack path analysis.8 releases · first seen Jul 2026▸
release
8 total
Redesigns the Attack Paths graph to group same-class resources into expandable nodes with counts and terminates every path in an explicit outcome node naming the destination impact: code execution, privilege escalation, public exposure, or resource inventory (Cloud/Private Cloud only).
5.39.0 · Aug 2026
· source
· release history
Attack Paths adds 20 AWS privilege-escalation detection queries from pathfinding.cloud, covering service iam:PassRole escalations across AWS Batch, Braket, Cognito Identity, ECS, EMR, EMR Serverless, GameLift, Glue, EC2 Image Builder, Kinesis Analytics, HealthOmics, EventBridge Scheduler, SSM, and Step Functions,…
5.38.0 · Aug 2026
· source
· release history
Attack Paths query metadata now exposes an outcome category (Code execution, Privilege escalation, Public exposure, or Resource inventory) on the queries endpoint, enabling terminal outcome nodes in the graph.
5.38.0 · Aug 2026
· source
· release history
Adds four AWS privilege-escalation Attack Path queries: STS-002 (cross-account role trust), STS-003 (wildcard role trust), IAM-022 (user permissions-boundary removal), and SSO-001 (IAM Identity Center permission-set escalation).
5.37.0 · Aug 2026
· source
· release history
Attack Paths query info panel now links every query to its page on Prowler Hub.
5.37.0 · Aug 2026
· source
· release history
Attack Paths query selector now hides confirmed-empty queries for the selected scan, surfacing only paths that returned data; full catalog published on Prowler Hub.
5.36.0 · Jul 2026
· source
· release history
+E2E Networks provider scanningverifiedsuggestedScans E2E Networks accounts for misconfigurations across compute, networking, security groups, load balancers, storage, and managed databases.2 releases · 6 other sources · first seen Jul 2026▸
Suggested capability: Credentialed vulnerability scanning. This is our guess, not confirmed.
release
New provider: Scans E2E Networks with 27 checks covering compute nodes, networking, security groups, load balancers, block/file storage, and managed databases.
5.34.0 · Jul 2026
· source
· release history
New provider: Scans E2E Networks with 27 checks covering compute nodes, networking, security groups, load balancers, block/file storage, and managed databases.
5.34.0 · Jul 2026
· source
· release history
command line
--e2e-networks-api-key — E2E Networks API key. Use E2E_NETWORKS_API_KEY env var instead of passing directly.
5.34.0 · Jul 2026
· command-line history
--e2e-networks-project-id — E2E Networks project ID. Use E2E_NETWORKS_PROJECT_ID env var instead of passing directly.
5.34.0 · Jul 2026
· command-line history
--e2e-networks-auth-token — E2E Networks auth token. Use E2E_NETWORKS_AUTH_TOKEN env var instead of passing directly.
5.34.0 · Jul 2026
· command-line history
example
Scan your E2E Networks environment for misconfigurations across compute, networking, and storage after setting your API credentials.$ export E2E_NETWORKS_API_KEY="your-api-key" export E2E_NETWORKS_AUTH_TOKEN="your-auth-token" export E2E_NETWORKS_PROJECT_ID="your-project-id" prowler e2enetworks
5.34.0 · Jul 2026
· source
Scan your E2E Networks environment for misconfigurations across compute, networking, storage, and managed databases.$ export E2E_NETWORKS_API_KEY="your-api-key" export E2E_NETWORKS_AUTH_TOKEN="your-auth-token" export E2E_NETWORKS_PROJECT_ID="your-project-id" prowler e2enetworks
5.34.0 · Jul 2026
· source
+AWS Application Load Balancer security checksshippedChecks that AWS Application Load Balancers are configured to drop malformed HTTP headers, reducing exposure to HTTP desync attacks.5 releases · 3 other sources · first seen Sep 2017▸
release
New AWS check elbv2_alb_drop_invalid_header_fields_enabled verifies Application Load Balancers drop invalid HTTP header fields to mitigate HTTP desync attacks (AWS FSBP ELB.4).
5.30.0 · Jun 2026
· source
· release history
New AWS check elbv2_alb_drop_invalid_header_fields_enabled verifies Application Load Balancers drop invalid HTTP header fields to mitigate HTTP desync attacks (FSBP ELB.4).
5.30.0 · Jun 2026
· source
· release history
Added extra7155 check for ALB desync mitigation mode.
2.6.0 · Nov 2021
· source
· release history
Adds -n CLI argument to show numeric check numbers (e.g., 1.02) in output for easier sorting
1.4 · Sep 2017
· source
· release history
Adds --max-items option to the extra72 subcommand to limit the number of items displayed
1.4 · Sep 2017
· source
· release history
example
Run the new ALB and SageMaker checks in isolation to validate specific FSBP and AI workload controls without a full scan.$ prowler aws --check elbv2_alb_drop_invalid_header_fields_enabled sagemaker_models_monitor_enabled
5.30.0 · Jun 2026
· source
Use numeric IDs for programmatic filtering of specific checks.$ prowler s3 -n | grep "1.02"
1.4 · Sep 2017
· source
Limit extra72 output to the top 5 critical items to reduce CI noise.$ prowler s3 --extra-72 --max-items 5
1.4 · Sep 2017
· source
+Okta DISA STIG compliance checksshippedRuns checks across Okta user accounts, authenticators, identity providers, network zones, API tokens, and system logs against the DISA Okta IDaaS STIG V1R2 framework.6 releases · 2 other sources · first seen Jul 2025▸
release
Adds complete DISA Okta IDaaS STIG V1R2 framework coverage for the Okta provider, spanning six new services: user, authenticator, idp, network, apitoken, and systemlog with 17 new checks covering account inactivity, MFA hardening, password policy, smart card, API token privilege, network zone enforcement,…
5.30.0 · Jun 2026
· source
· release history
Adds complete DISA Okta IDaaS STIG V1R2 framework coverage with 18 new checks spanning user inactivity, password policy, MFA hardening, smart card, network zones, API tokens, and system log streaming.
5.30.0 · Jun 2026
· source
· release history
Adds Okta provider support in Prowler App with OAuth 2.0 private-key JWT credentials, enabling read-only scanning of Okta tenants from the UI.
5.28.0 · May 2026
· source
· release history
Adds four new medium-severity Okta DISA STIG V1R2 checks: signon_global_session_lifetime_18h, signon_global_session_cookies_not_persistent, signon_global_session_policy_network_zone_enforced, and signon_dod_warning_banner_configured.
5.28.0 · May 2026
· source
· release history
New Okta provider (CLI-only): authenticate via OAuth read-only credentials and audit your Okta tenant; ships with signon_global_session_idle_timeout_15min mapped to DISA STIG V-273186.
5.27.0 · May 2026
· source
· release history
Enforces stronger password requirements for new sign-ups: minimum 12 characters with uppercase, lowercase, numbers, and special characters, with a real-time strength indicator.
5.9.0 · Jul 2025
· source
· release history
example
Run all Okta DISA STIG V1R2 checks against your Okta tenant to assess compliance posture end-to-end.$ prowler okta --compliance disa_okta_idaas_stig_v1r2_okta
5.30.0 · Jun 2026
· source
Audit an Okta tenant for DISA STIG session policy compliance in minutes using OAuth read-only credentials.$ export OKTA_ORG_DOMAIN="your-tenant.okta.com" export OKTA_CLIENT_ID="0oa1234567890abcdef" export OKTA_PRIVATE_KEY_FILE="/path/to/prowler-okta.pem" prowler okta
5.27.0 · May 2026
· source
+Resource evidence metadatashippedSurfaces raw resource attributes captured at scan time directly within the finding detail view and API.6 releases · 2 other sources · first seen Jan 2025▸
release
New Resource Metadata / Evidence tab in the Prowler App finding detail drawer surfaces raw resource attributes captured at scan time, backed by the new resource.metadata attribute on /api/v1/findings?include=resources.
5.28.0 · May 2026
· source
· release history
AWS findings and resource details in the Prowler App now include a one-click View in AWS Console link via the /go/view ARN resolver.
5.27.0 · May 2026
· source
· release history
Resources page gains batch-applied filters, syntax-highlighted metadata JSON, and a View Resource button from finding detail drawers.
5.25.0 · Apr 2026
· source
· release history
Redesigned resource detail side drawer consolidates metadata, findings, and event timeline in a single panel for in-context investigation.
5.24.0 · Apr 2026
· source
· release history
UI: Finding details layout redesigned to include first_seen timestamp.
5.2.0 · Jan 2025
· source
· release history
Findings now carry a first_seen_at field to track when Prowler first observed each finding.
5.2.0 · Jan 2025
· source
· release history
example
Fetch the latest scan results for all resources to build an up-to-date asset inventory.$ curl -X GET https://<prowler-api>/resources/latest \ -H 'Authorization: Bearer <token>'
5.9.0 · Jul 2025
· source
Inspect full resource metadata (ARN, region, config details) for every finding in OCSF format.$ prowler --output-format json-ocsf
5.2.0 · Jan 2025
· source
+Enhanced threat posture visualizationshippedExpands security dashboards with Attack Surface metrics, Risk Pipeline and Threat Map charts, and ThreatScore visualizations to monitor risk trends.8 releases · first seen Nov 2025▸
release
8 total
Adds clickable ThreatScore pillars on /compliance that jump to the detail page with the selected accordion pre-expanded and scrolled into view.
5.26.0 · May 2026
· source
· release history
ThreatScore pillar breakdown added to the Compliance Summary page, showing per-pillar (Identity, Data Protection, Network Security, etc.) contribution to overall risk score.
5.17.0 · Jan 2026
· source
· release history
Adds Risk Radar component with category-based severity breakdown to the Overview page in the UI.
5.16.0 · Dec 2025
· source
· release history
New API endpoint to retrieve an overview of attack surfaces.
5.15.0 · Dec 2025
· source
· release history
New Overview dashboard panels: Attack Surface (internet-facing resources, leaked secrets, privilege-escalation paths), Service Watchlist, Findings Severity Over Time, Risk Pipeline (Sankey chart), Threat Map (region-based pass/fail ratios), and Risk Plot (severity-weighted Threat Score visualization).
5.15.0 · Dec 2025
· source
· release history
Adds new endpoint GET /api/v1/overview/regions to retrieve aggregated findings data by region.
5.14.0 · Nov 2025
· source
· release history
+JSON output format supportshippedEnables scanning results to be exported in JSON format for integration into CI/CD pipelines and other automation workflows.7 releases · 1 other source · first seen Nov 2018▸
Also counts toward: CI/CD pipeline integration, Command-line interface, CSV data export, JSON data export
release
7 total
The .ocsf.json output now includes check_id, compliance, and full check metadata in OCSF Detection Findings.
4.1.0 · Apr 2024
· source
· release history
JSON output now follows the OCSF Schema v1.1.0 format
4.0.0 · Apr 2024
· source
· release history
Adds OCSF JSON as a default output format for AWS, Azure, and GCP scanners to integrate with platforms like Amazon Security Lake
3.6.0 · Jun 2023
· source
· release history
Enables HTML, CSV, and JSON output files automatically on every run
3.0.0 · Dec 2022
· source
· release history
Generates consolidated CSV and JSON reports with over 40 values per finding
3.0.0 · Dec 2022
· source
· release history
Adds -V flag to display the current version
2.0 · Nov 2018
· source
· release history
example
Produce a SARIF report from an IaC scan for direct import into GitHub Code Scanning or any SARIF-compatible tool.$ prowler iac --output-formats sarif
5.25.0 · Apr 2026
· source
+Multi-region scan supportshippedAllows scanning specific comma-separated AWS regions in a single invocation rather than running separate scans for each region.4 releases · 4 other sources · first seen Mar 2022▸
Also counts toward: Command-line interface
release
Adds --excluded-region CLI flag, PROWLER_AWS_DISALLOWED_REGIONS environment variable, and aws.disallowed_regions config key to exclude specific AWS regions from scans.
5.24.0 · Apr 2026
· source
· release history
OCI multi-region filtering via --region now covers filestorage, blockstorage, kms, compute, and identity services including regions outside the tenancy home region.
5.23.0 · Apr 2026
· source
· release history
Adds support for AWS European Sovereign Cloud regions, enabling data-residency-constrained organizations to run Prowler security scans.
5.17.0 · Jan 2026
· source
· release history
Adds --filter-region support for comma-separated regions to scan multiple specific regions in one run
2.8.0 · Mar 2022
· source
· release history
example
Scope an AWS scan to only your active regions by excluding regions you don't use, keeping results focused and scan time down.$ prowler aws --excluded-region us-west-1 --excluded-region ap-northeast-3
5.24.0 · Apr 2026
· source
Exclude multiple regions globally via environment variable in CI pipelines without modifying command-line invocations.$ export PROWLER_AWS_DISALLOWED_REGIONS="eu-south-1,ap-east-1" prowler aws
5.24.0 · Apr 2026
· source
Filter an OCI scan to specific regions (including regions outside the tenancy home region) using the new multi-region support.$ prowler oci --region us-ashburn-1 eu-frankfurt-1 --service filestorage kms compute
5.23.0 · Apr 2026
· source
Scan two specific AWS regions (eu-west-1 and us-east-2) in a single invocation instead of running twice.$ prowler --profile my-profile --filter-region eu-west-1,us-east-2
2.8.0 · Mar 2022
· source
+Partial resource-scoped scanningshippedAllows launching a scan against up to 10 specific resources by UID — from the Findings page, the resource detail drawer, or the API — so a just-remediated resource can be re-checked immediately without waiting for the next full scan.4 releases · 3 other sources · first seen Sep 2026▸
Also counts toward: REST API
release
Adds POST /api/v1/scans support for resource_uids (up to 10 resources) to launch partial scans, with is_partial exposed on scan objects and a filter[is_partial] query parameter on scan list endpoints.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
5.44.0 · Sep 2026
· source
· release history
Adds a Re-check resource action in the Findings page actions menu and resource detail drawer, launching a partial scan that re-runs only the checks that last reported on that resource.
5.44.0 · Sep 2026
· source
· release history
Adds Re-check resource action in the Findings page (actions menu, resource detail drawer, and hint icon next to Last seen) to launch a partial scan on a just-remediated resource without waiting for the next full scan.
5.44.0 · Sep 2026
· source
· release history
Adds POST /api/v1/scans support for resource_uids (up to 10 resources) to launch a partial scan against specific resources, with is_partial field and filter[is_partial] filter on scan endpoints.
5.44.0 · Sep 2026
· source
· release history
docs
September 29, 2026 Findings — Re-check a Resource with a Partial Scan A resource that has just been fixed can be confirmed from the Findings page without waiting for the next full scan.
docs update · Sep 2026
· source
September 29, 2026 🔁 Findings — Re-check a Resource with a Partial Scan A resource that has just been fixed can be confirmed from the Findings page without waiting for the next full scan.
seen Sep 2026
· source
example
Immediately re-check up to 10 specific resources after a remediation, without waiting for the next full scan.$ curl -X POST https://<your-prowler-api>/api/v1/scans \ -H 'Authorization: Bearer <token>' \ -H 'Content-Type: application/json' \ -d '{"resource_uids": ["arn:aws:s3:::my-bucket",…
5.44.0 · Sep 2026
· source
+M365 Conditional Access and Admin Center security checksshippedChecks Microsoft 365 Conditional Access policies for Azure DevOps targeting, exclusion gaps, deleted object references, and group management restrictions.7 releases · first seen Jun 2026▸
Adds defender_priority_account_protection_enabled and defender_strict_preset_security_policy_enabled checks for M365 provider, covering CIS M365 Foundations Benchmark v7.0.0 controls 2.4.1 and 2.4.2.
5.38.0 · Aug 2026
· source
· release history
Adds admincenter_shared_bookings_disabled check for M365 provider, covering CIS Microsoft 365 Foundations Benchmark v7.0.0 control 1.3.9.
5.38.0 · Aug 2026
· source
· release history
Adds teams_external_access_trial_tenants_blocked check for M365 provider, covering CIS M365 Foundations Benchmark v7.0.0 control 8.2.4.
5.38.0 · Aug 2026
· source
· release history
Adds exchange_owa_mailbox_policy_personal_accounts_disabled and exchange_organization_reject_direct_send_enabled checks for M365 provider, covering CIS M365 Foundations Benchmark v7.0.0 controls 6.3.2 and 6.5.5.
5.38.0 · Aug 2026
· source
· release history
New Microsoft 365 Conditional Access check entra_conditional_access_policy_explicitly_targets_azure_devops: verifies at least one enabled policy explicitly includes the Azure DevOps cloud application.
5.32.0 · Jul 2026
· source
· release history
New Microsoft 365 Conditional Access checks: entra_conditional_access_policy_explicitly_targets_azure_devops and entra_conditional_access_policy_no_exclusion_gaps, plus Entra Conditional Access group management restriction check.
5.32.0 · Jul 2026
· source
· release history
+Kubernetes provider Cloud security hardeningshippedRejects kubeconfigs using exec authentication in Prowler Cloud to prevent user-supplied commands from executing on Cloud workers.6 releases · 1 other source · first seen Feb 2025▸
release
Rejects kubeconfig files using legacy auth-provider.config.cmd-path command authentication in Kubernetes credential forms
5.36.0 · Jul 2026
· source
· release history
Kubernetes provider rejects kubeconfigs using exec authentication in Prowler Cloud, blocking user-supplied commands from executing on Cloud workers.
5.33.0 · Jul 2026
· source
· release history
Rejects kubeconfigs using exec authentication for the Kubernetes provider in Prowler Cloud, preventing user-supplied commands from executing on Cloud workers.
5.33.0 · Jul 2026
· source
· release history
Supports HTTPS_PROXY and K8S_SKIP_TLS_VERIFY environment variables for Kubernetes provider.
5.8.0 · Jul 2025
· source
· release history
Supports setting cluster name in in-cluster mode for Kubernetes provider.
5.7.0 · May 2025
· source
· release history
Increased allowed provider UID length for Kubernetes providers to support AWS EKS, Azure AKS, and GCP GKE.
5.3.0 · Feb 2025
· source
· release history
docs
Only inline kubeconfig credentials are supported: token username password , or client-certificate-data with client-key-data for users, and certificate-authority-data for clusters.
seen Oct 2026
· source
+Custom Docker image buildsshippedsuggestedAllows users to build custom Prowler images and run the tool within AWS Fargate using container metadata for authentication.5 releases · 2 other sources · first seen Jan 2018▸
Suggested capability: Infrastructure-as-code security scanning. This is our guess, not confirmed.
release
Publishes multi-architecture Docker images (linux/amd64 and linux/arm64) to Docker Hub.
5.14.0 · Nov 2025
· source
· release history
Full platform now deployable on-premises via docker compose up -d, serving the UI at https://localhost:3000.
5.0.0 · Dec 2024
· source
· release history
Enables scanning an entire AWS account across all regions up to 37x faster
3.0.0 · Dec 2022
· source
· release history
Adds support for running Prowler on AWS Fargate using metadata for credentials
2.0 · Nov 2018
· source
· release history
Adds new Dockerfile to build custom Prowler images
1.5 · Jan 2018
· source
· release history
example
Stand up the full Prowler platform locally — UI, API, and persistent storage — without any cloud dependency.$ docker compose up -d
5.0.0 · Dec 2024
· source
Build a custom Prowler Docker image using the provided Dockerfile.$ docker build -t my-prowler .
1.5 · Jan 2018
· source
+Targeted check executionshippedEnables users to define a specific list of checks to run via an input file rather than executing the full suite.4 releases · 3 other sources · first seen Nov 2021▸
release
Adds --custom-checks-metadata-file <path> to allow overriding check metadata via YAML.
4.2.0 · May 2024
· source
· release history
Adds --custom-checks-metadata-file CLI flag to override check severity via an external YAML file
3.12.0 · Jan 2024
· source
· release history
prowler aws --list-checks-json lists all available checks in JSON format for use with --checks-file
3.9.0 · Aug 2023
· source
· release history
-C <file> allows providing a file of checks to be ran.
2.6.0 · Nov 2021
· source
· release history
example
Override metadata for custom checks using a YAML file.$ prowler aws --custom-checks-metadata-file custom_checks_metadata.yaml
4.2.0 · May 2024
· source
Override severity for specific checks using an external metadata file instead of modifying source code.$ prowler aws --custom-checks-metadata-file custom_checks_metadata.yaml
3.12.0 · Jan 2024
· source
Run Prowler against a custom directory of user-defined security checks$ prowler aws -x /path/to/custom/checks
3.4.0 · Apr 2023
· source
+Concurrent scan queuingshippedQueues overlapping scans for the same provider behind the active scan instead of running them concurrently, preventing duplicate or racing scan workers.6 releases · first seen Jan 2025▸
release
Unifies latest-scan resolution across all endpoints so findings, compliance, and mute rules always read from the same scan when overlapping scans exist.
5.44.0 · Sep 2026
· source
· release history
Unifies latest-scan resolution across all endpoints so findings, compliance, and mute rules always read from the same scan for a given provider.
5.44.0 · Sep 2026
· source
· release history
Adds scan queueing: overlapping scans for the same provider now queue behind the active scan instead of running concurrently.
5.33.0 · Jul 2026
· source
· release history
Overlapping scans for the same provider now queue behind the active scan instead of running concurrently, eliminating duplicate or racing scan workers.
5.33.0 · Jul 2026
· source
· release history
Adds a new background queue for backfill tasks in the API.
5.7.0 · May 2025
· source
· release history
Adds configurable broker visibility timeout setting for the Celery task queue.
5.1.0 · Jan 2025
· source
· release history
+AI agent tutorials and programmatic access guidanceshippedProvides in-app tutorials and a banner guiding users through connecting AI agents to Prowler Cloud via the API to query and act on security posture programmatically.3 releases · 3 other sources · first seen Jul 2026▸
release
Expired invitations are now re-invitable: a pending invitation past its expiry is marked expired and a new invitation is created for the same email rather than returning a generic error; filter[state__in] on the invitations endpoint no longer returns a server error.
5.43.0 · Sep 2026
· source
· release history
Adds browser-based Import Findings dialog on the Scans page (Prowler Cloud and Private Cloud) accepting .ocsf.json reports via drag-and-drop or file picker, with inline job-completion and error reporting (requires Manage Ingestions permission).
5.41.0 · Sep 2026
· source
· release history
New AI agents tutorials and overview banner guide users through connecting AI agents to Prowler Cloud via the API to query and act on security posture programmatically.
5.36.0 · Jul 2026
· source
· release history
docs
- [Import Findings](https://docs.prowler.com/user-guide/tutorials/prowler-import-findings.md): Upload OCSF scan results to Prowler Cloud from the UI, the CLI or the API - [Boto3 Retrier and Timeout Configuration in Prowler](https://docs.prowler.com/user-guide/providers/aws/boto3-configuration.md)
docs update · Sep 2026
· source
September 2, 2026 Scans — Import Findings from the Browser Findings produced outside the platform, by the Prowler CLI or a CI pipeline, can now be brought into the app without leaving the browser.
docs update · Sep 2026
· source
- [Prowler for MSPs and MSSPs](https://docs.prowler.com/getting-started/products/prowler-for-msps.md) - [Connect Claude Code to Prowler MCP Server](https://docs.prowler.com/user-guide/ai-agents/claude-code.md) - [Connect the Claude App Chat to Prowler MCP…
docs update · Jul 2026
· source
+Jira finding and finding-group exportshippedSends selected findings or Finding Groups to Jira as one grouped issue or as separate issues, with deep links and filter context preserved.4 releases · 2 other sources · first seen Apr 2025▸
Also counts toward: Ticketing integration
release
Enables linking from Jira issues to Prowler findings by setting the DJANGO_UI_BASE_URL environment variable in the Local Server API
5.41.0 · Sep 2026
· source
· release history
Adds prowler_send_findings_to_jira MCP tool gains Cloud-only grouped dispatch: select failed findings by check IDs against the latest completed scan and send one Jira work item per check listing up to 50 affected resources, with per-group error reporting.
5.39.0 · Aug 2026
· source
· release history
Grouped Jira workflows (Prowler Cloud/Private Cloud): send selected findings or Finding Groups to Jira as one grouped issue or separate issues, with deep links and filter context preserved.
5.36.0 · Jul 2026
· source
· release history
Adds basic authentication support to the SDK Jira integration.
5.5.0 · Apr 2025
· source
· release history
docs
July 24, 2026 Finding Groups - Jira This feature is available exclusively in Prowler Cloud and Prowler Private Cloud with a subscription . Selected Findings, Finding Groups, and mixed selections can now be sent to Jira. When you select multiple findings, choose between one grouped issue or separate issues.
docs update · Aug 2026
· source
example
Enable finding-to-issue deep links in Jira by pointing the API at your Prowler Cloud UI base URL.$ DJANGO_UI_BASE_URL=https://cloud.prowler.com
5.41.0 · Sep 2026
· source
+Shodan external exposure enrichmentshippedsuggestedIntegrates Shodan API to identify publicly exposed cloud resources such as Elastic IPs during scan execution.4 releases · 2 other sources · first seen Apr 2021▸
Suggested capability: Log enrichment. This is our guess, not confirmed.
Also counts toward: Command-line interface
release
New rolesanywhere_profile_restricts_session_permissions check flags IAM Roles Anywhere profiles that reference an administrative role without scoping down vended sessions via a session policy or managed policies.
5.40.0 · Aug 2026
· source
· release history
Adds --shodan <API_KEY> CLI flag to check if public IPs in Azure or GCP are exposed on Shodan
3.15.0 · Mar 2024
· source
· release history
Adds support for setting the Shodan API key via the config.yaml file instead of a CLI flag
3.15.0 · Mar 2024
· source
· release history
Adds -N <shodan_api_key> CLI argument to run extra7102 (Elastic IP Shodan check)
2.4.0 · Apr 2021
· source
· release history
example
Scan GCP compute resources and cross-reference them with Shodan to find publicly exposed addresses.$ prowler gcp -c compute_public_address_shodan --shodan <API_KEY>
3.15.0 · Mar 2024
· source
Check for exposed Elastic IPs using Shodan's API to enrich risk assessment.$ prowler -N your_shodan_api_key extra7102
2.4.0 · Apr 2021
· source
+Active tenant identification in APIshippedThe users/me API endpoint marks the active tenant for both JWT and API key authentication so clients can identify which tenant is in use.6 releases · first seen Mar 2025▸
Also counts toward: REST API
release
Updates GET /api/v1/users/me to use meta.active for identifying the active tenant in membership relationships for JWT and API key authentication
5.39.0 · Aug 2026
· source
· release history
Adds GET /api/v1/users/me membership relationships now identify the active tenant with meta.active for both JWT and API key authentication.
5.39.0 · Aug 2026
· source
· release history
GET /api/v1/users/me membership relationships now use meta.active for active tenant identification; existing clients parsing previous location may need updates
5.39.0 · Aug 2026
· source
· release history
Tenant owners can now expel users from their organizations via the UI or DELETE /tenants/{tenant_pk}/memberships/{id}, immediately blacklisting outstanding refresh tokens.
5.25.0 · Apr 2026
· source
· release history
Adds social login via Google and GitHub for Prowler App authentication.
5.5.0 · Apr 2025
· source
· release history
Adds social login integration with Google and GitHub to the API.
5.4.0 · Mar 2025
· source
· release history
+Reusable scan configuration managementshippedAllows creation of named, schema-validated YAML scan configurations in Prowler Cloud that can be attached to one or more providers for consistent reuse.6 releases · first seen Feb 2025▸
Also counts toward: Web management console
release
Adds excluded_checks and excluded_services fields to scan configurations, allowing entire checks or services to be skipped per provider for faster, lower-noise scans.
5.35.0 · Jul 2026
· source
· release history
Prowler Cloud/Enterprise: Scan Configuration management page enables named, reusable YAML scan configs validated against a per-provider schema and attachable to one or more providers.
5.32.0 · Jul 2026
· source
· release history
Adds named, reusable scan configurations in Prowler Cloud/Enterprise via a dedicated Scans / Configuration page, backed by YAML that follows prowler/config/config.yaml structure with per-provider type-safe validation.
5.32.0 · Jul 2026
· source
· release history
Supports Microsoft 365 app-only (service principal) authentication via OAuth 2.0 client-credentials, enabling fully unattended scans against Exchange Online, SharePoint, Teams, etc.
5.8.0 · Jul 2025
· source
· release history
The encrypted_password field is renamed to password for the M365 provider.
5.7.3 · Jun 2025
· source
· release history
Adds Microsoft365 as a new cloud provider with three authentication methods: service principal, Azure CLI, and interactive browser.
5.3.0 · Feb 2025
· source
· release history
+Prowler Cloud scan schedulingshippedAllows per-provider scan scheduling at daily, 48-hour, weekly, or monthly cadences from the Providers page in Prowler Cloud.6 releases · first seen Apr 2025▸
Also counts toward: Scheduled jobs
release
Prowler Cloud: flexible per-provider scan scheduling with Daily, Every 48 hours, Weekly, or Monthly cadences configurable from the Providers page.
5.31.0 · Jun 2026
· source
· release history
Flexible per-provider scan scheduling in Prowler Cloud with daily, 48-hour, weekly, and monthly cadence options via the Providers page and a new Scheduled tab in Scan Jobs.
5.31.0 · Jun 2026
· source
· release history
Redesigns the Scan Jobs UI view with dedicated In Progress, Completed, and Scheduled tabs and a new scan-launch modal for picking accounts and adding scan notes.
5.29.0 · Jun 2026
· source
· release history
POST /schedules/daily now returns 409 CONFLICT if a daily schedule already exists.
5.9.0 · Jul 2025
· source
· release history
Adds one-time scan execution support in the UI.
5.5.0 · Apr 2025
· source
· release history
Adds option to skip scheduling the daily scan when onboarding a new provider, enabling one-time or manually triggered scans.
5.5.0 · Apr 2025
· source
· release history
+Resource Groups visualizationshippedAggregates cloud resources by security-relevant categories such as Compute, Storage, Network, and Identity with finding severity breakdowns.4 releases · 2 other sources · first seen Jan 2025▸
release
Overview endpoints (/overviews/resource-groups, /overviews/categories, /overviews/attack-surfaces) now reflect newly muted findings immediately without waiting for the next scan.
5.25.0 · Apr 2026
· source
· release history
New Resource Groups Overview aggregates cloud resources by security-relevant categories (Compute, Storage, Network, Identity) with finding severity breakdowns via new /api/v1/overviews/resource-groups endpoint.
5.17.0 · Jan 2026
· source
· release history
New category overview endpoint provides severity breakdowns by security domain across your environment.
5.16.0 · Dec 2025
· source
· release history
Adds GET /overviews/services API endpoint for service-level overviews.
5.1.0 · Jan 2025
· source
· release history
example
Retrieve the resource groups security overview to identify which categories have the most critical findings.$ curl -s 'https://<your-prowler-api>/api/v1/overviews/resource-groups' -H 'Authorization: Bearer <token>'
5.17.0 · Jan 2026
· source
Filter findings by category via the API to feed a downstream dashboard focused on a specific security domain.$ curl -s -H "Authorization: Bearer <token>" "https://<api-host>/api/v1/findings/latest?category=privilege-escalation"
5.16.0 · Dec 2025
· source
+Findings Grouped ViewshippedCollapses repeated misconfigurations into single rows with impacted resource counters and inline expansion capabilities.5 releases · 1 other source · first seen May 2025▸
release
Syntax highlighting for remediation code blocks in the finding groups drawer with provider-aware auto-detection of Shell, HCL, YAML, and Bicep.
5.24.0 · Apr 2026
· source
· release history
Findings Grouped View in the UI collapses repeated misconfigurations into one row per check with an X-of-Y impacted resources counter, inline resource expansion, bulk-mute, and an Other Findings For This Resource tab in the detail drawer.
5.23.0 · Apr 2026
· source
· release history
New batch-apply filter pattern on the Findings page — configure multiple filters before executing, eliminating per-selection API calls and layout shifts.
5.22.0 · Mar 2026
· source
· release history
Redesigned findings table with improved multi-select filtering UX, enhanced table interactions, and resource group filter integration.
5.17.0 · Jan 2026
· source
· release history
Finding URLs in the UI now include the finding ID, enabling direct sharing within an organization.
5.6.0 · May 2025
· source
· release history
example
Filter findings by resource group (e.g., only Compute resources) to triage the highest-risk category after upgrading.$ curl -s 'https://<your-prowler-api>/api/v1/findings?group=Compute' -H 'Authorization: Bearer <token>'
5.17.0 · Jan 2026
· source
+Third-party compliance and security framework checksshippedAdds support for checking controls across ENS, FFIEC, SOC2, HIPAA, and GDPR frameworks alongside existing cloud provider checks.6 releases · first seen Apr 2021▸
release
Adds Processing Integrity requirements to the SOC 2 compliance framework for AWS, Azure, and GCP providers.
5.15.0 · Dec 2025
· source
· release history
Adds SOC2 compliance framework assessment for Azure (prowler azure --compliance soc2_azure), matching existing AWS and GCP SOC2 support.
5.6.0 · May 2025
· source
· release history
Adds SOC 2 compliance framework for GCP and ISO 27001:2022 for Azure, GCP, and Kubernetes.
5.5.0 · Apr 2025
· source
· release history
Adds 17 new AWS security compliance frameworks including CISA Cyber Essentials, FedRAMP Low/Mod, FFIEC, GDPR, HIPAA, NIST CSF/800-171/800-53, PCI v3.2.1, and SOC 2.
3.2.0 · Feb 2023
· source
· release history
Adds new Spanish ENS compliance framework support
3.0.0 · Dec 2022
· source
· release history
Adds new checks for SageMaker, ENS (Esquema Nacional de Seguridad), FFIEC, SOC2, and additional HIPAA/GDPR controls
2.4.0 · Apr 2021
· source
· release history
+Scan resource volume cappingshippedLimits the number of resources analysed per high-volume AWS service globally or per service to control scan duration and cost.4 releases · 1 other source · first seen Jul 2026▸
release
Adds DJANGO_OUTPUT_S3_AWS_ENDPOINT_URL environment variable to point scan output uploads and downloads at S3-compatible object storage such as MinIO, without hijacking process-wide AWS API calls.
5.44.0 · Sep 2026
· source
· release history
Adds DJANGO_OUTPUT_S3_AWS_ENDPOINT_URL environment variable to direct scan output uploads and downloads at S3-compatible object storage such as MinIO, without polluting process-wide AWS environment variables.
5.44.0 · Sep 2026
· source
· release history
Adds per-service resource caps for large AWS accounts: global max_scanned_resources_per_service plus per-service overrides for EBS snapshots, Backup recovery points, CloudWatch log groups, Lambda functions, ECS task definitions, and CodeArtifact packages.
5.32.0 · Jul 2026
· source
· release history
AWS scans can now cap the number of resources analyzed per high-volume service via max_scanned_resources_per_service (global) or per-service limits: max_ebs_snapshots, max_backup_recovery_points, max_cloudwatch_log_groups, max_lambda_functions, max_ecs_task_definitions, max_codeartifact_packages.
5.32.0 · Jul 2026
· source
· release history
example
Scan specific services only$ prowler aws --services s3 iam
+Third-party OCSF report importshippedAllows users to upload scan results in OCSF format from external cyber tooling into the platform for centralized tracking and reporting.3 releases · 2 other sources · first seen Mar 2026▸
Also counts toward: CI/CD pipeline integration, Command-line interface, REST API, Web management console
release
Adds Import Findings dialog on the Scans page to upload .ocsf.json reports via drag-and-drop or file picker in Prowler Cloud/Private Cloud
5.41.0 · Sep 2026
· source
· release history
New POST /api/v1/ingestions API endpoint enables CI/CD pipelines to import scan findings into Prowler Cloud.
5.19.0 · Mar 2026
· source
· release history
New --push-to-cloud CLI flag uploads findings in OCSF format directly to Prowler Cloud for centralized visibility.
5.19.0 · Mar 2026
· source
· release history
docs
- [Import Findings](https://docs.prowler.com/user-guide/tutorials/prowler-import-findings.md): Upload OCSF scan results to Prowler Cloud from the UI, the CLI or the API
docs update · Sep 2026
· source
example
Push findings from an existing CLI scan to Prowler Cloud for centralized correlation and reporting.$ prowler aws --push-to-cloud
5.19.0 · Mar 2026
· source
+Alerts and digest managementshippedsuggestedProvides auto-provisioned daily critical findings digests and custom alert rules scoped by provider, account, severity, or status.4 releases · 1 other source · first seen Apr 2025▸
Suggested capability: Log routing. This is our guess, not confirmed.
release
Slack workspace integration (Prowler Cloud / Prowler Private Cloud): connect a workspace from the Integrations page, authorize destination channels, and select them in alert rules alongside email recipients; the alerts list shows both in a unified Destinations column.
5.40.0 · Aug 2026
· source
· release history
Adds Manage Alerts RBAC permission to gate alert configuration to authorized organization admins.
5.26.0 · May 2026
· source
· release history
Adds Prowler Cloud Alerts: auto-provisioned daily digest of critical findings for organization owners, plus custom alert rules scoped by provider, account, severity, or status, with a Create Alert shortcut that converts active Findings page filters into a watching alert rule.
5.26.0 · May 2026
· source
· release history
Adds static service status icon with link to the status page in the UI.
5.5.0 · Apr 2025
· source
· release history
docs
- [Alerts](https://docs.prowler.com/user-guide/tutorials/prowler-alerts.md): Create alerts from Prowler Cloud findings, deliver them to email recipients and Slack channels, and monitor relevant security changes after scans or in daily digests.
docs update · Aug 2026
· source
+Compliance framework configuration-aware evaluationshippedMarks compliance requirements as FAIL when the check ran under a configuration too permissive to satisfy the requirement, reflected in CSV, OCSF, and console outputs.5 releases · first seen Feb 2020▸
Also counts toward: CSV data export
release
Adds Resolved triage status for MANUAL findings in Prowler Cloud, recording written evidence and verifying the finding as an effective PASS for 90 days or until a real failure is detected (Cloud/Private Cloud only).
5.39.0 · Aug 2026
· source
· release history
Populates finding_info.analytic and finding_info.attacks in OCSF detection finding output with Prowler check rules and MITRE ATT&CK technique/tactic objects for findings that carry MITRE ATT&CK compliance metadata.
5.37.0 · Aug 2026
· source
· release history
Adds ConfigRequirements support on compliance framework requirements so a requirement reports FAIL when mapped checks ran under a configuration too loose to satisfy it, reflected across CSV, OCSF, and console outputs.
5.32.0 · Jul 2026
· source
· release history
Compliance frameworks can now declare ConfigRequirements on a requirement, marking it FAIL when mapped checks ran under a configuration too permissive to satisfy it — reflected in CSV, OCSF, and console outputs.
5.32.0 · Jul 2026
· source
· release history
megaprowler code for multi-account scanning (sample implementation)
2.2.0 · Feb 2020
· source
· release history
+AWS SageMaker security and AI governance checksshippedVerifies that SageMaker monitoring schedules are active and that at least one Clarify explainability job exists per region.5 releases · first seen Jun 2026▸
Also counts toward: Scheduled jobs
release
Adds sagemaker_endpoint_config_kms_encryption_enabled check to verify SageMaker endpoint configurations use a KMS key for storage volume encryption.
5.37.0 · Aug 2026
· source
· release history
New AWS ML check: sagemaker_clarify_exists verifies at least one SageMaker Clarify processing job exists per region.
5.31.0 · Jun 2026
· source
· release history
New AWS ML check: sagemaker_clarify_exists verifies at least one SageMaker Clarify processing job exists per region for bias-detection and explainability controls.
5.31.0 · Jun 2026
· source
· release history
New AWS check sagemaker_models_monitor_enabled verifies each SageMaker monitoring schedule is in the Scheduled state to catch data and model drift.
5.30.0 · Jun 2026
· source
· release history
New AWS check sagemaker_models_monitor_enabled verifies each SageMaker monitoring schedule is in the Scheduled state to detect data and model drift.
5.30.0 · Jun 2026
· source
· release history
+S3-compatible object storage for scan outputshippedDirects scan report uploads and downloads to any S3-compatible object storage endpoint such as MinIO via an environment variable, without affecting process-wide AWS API calls or role assumptions.2 releases · 2 other sources · first seen Sep 2026▸
Also counts toward: S3 export, Self-hosted deployment
release
Enables report downloads from self-hosted storage via DJANGO_OUTPUT_S3_AWS_PUBLIC_ENDPOINT_URL environment variable
5.43.0 · Sep 2026
· source
· release history
Adds DJANGO_OUTPUT_S3_AWS_PUBLIC_ENDPOINT_URL environment variable to sign report download URLs against a browser-reachable storage host, enabling downloads on deployments where object storage is only reachable inside the container network.
5.43.0 · Sep 2026
· source
· release history
example
Point Prowler self-hosted scan output at a MinIO instance instead of AWS S3, keeping role-assumption calls unaffected.$ DJANGO_OUTPUT_S3_AWS_ENDPOINT_URL=http://minio.internal:9000
5.44.0 · Sep 2026
· source
Point a self-hosted Prowler deployment at MinIO (or another S3-compatible store) for scan report storage without affecting AWS provider role assumptions.$ DJANGO_OUTPUT_S3_AWS_ENDPOINT_URL=http://minio.internal:9000
5.44.0 · Sep 2026
· source
+Confused deputy prevention checksshippedChecks for IAM service role configurations to prevent confused deputy attacks using source ARN and account condition keys.3 releases · 1 other source · first seen Jan 2023▸
release
New check iam_role_service_trust_restricts_source_to_account flags IAM roles whose trust policy allows an AWS service principal to assume the role without a source-account constraint.
5.41.0 · Sep 2026
· source
· release history
AWS IAM Role External ID is now a mandatory field when configuring IAM Role authentication.
5.2.0 · Jan 2025
· source
· release history
Adds new AWS check iam_role_cross_service_confused_deputy_prevention to validate IAM Service Roles against confused deputy attacks.
3.1.0 · Jan 2023
· source
· release history
example
Explicitly run the confused deputy prevention check to ensure IAM roles use aws:SourceArn and aws:SourceAccount condition keys.$ prowler aws -c iam_role_cross_service_confused_deputy_prevention
3.1.0 · Jan 2023
· source
+Slack execution summariesshippedsuggestedSends scan execution summaries to Slack channels to facilitate team notification and visibility.2 releases · 2 other sources · first seen May 2023▸
Suggested capability: Log routing. This is our guess, not confirmed.
Also counts toward: Outbound webhooks (the product notifies you)
release
Slack integration connection check now displays its result (including the refused or reached channels) directly on the integration card, not only in a transient toast notification (Prowler Cloud only).
5.41.0 · Sep 2026
· source
· release history
Slack integration added to send execution summaries to a channel
3.5.0 · May 2023
· source
· release history
docs
August 28, 2026 Slack Integration — Alert Channel Destinations Alerts can now reach Slack. Connect a Slack workspace from the Integrations page, authorize one or several destination channels (the connection check confirms each channel with a one-time message and names any channel Slack refuses), and pick those…
docs update · Aug 2026
· source
- [Slack Integration](https://docs.prowler.com/user-guide/tutorials/prowler-app-slack-integration.md): Connect a Slack workspace to Prowler Cloud or Prowler Private Cloud, choose the channel Prowler posts to, and verify the connection.
docs update · Aug 2026
· source
+StackIT provider scanningshippedScans StackIT sovereign cloud accounts via service account key file or inline JSON for security misconfigurations.3 releases · 1 other source · first seen Jun 2026▸
Also counts toward: CI/CD pipeline integration, Command-line interface
release
New ske_cluster_no_public_endpoint check (STACKIT) flags SKE clusters whose Kubernetes API endpoint is publicly reachable because the ACL extension is disabled or its allowed CIDR list contains 0.0.0.0/0 or ::/0.
5.40.0 · Aug 2026
· source
· release history
New STACKIT check iaas_server_public_ip_attached: flags IaaS servers with a public IP address directly attached to a network interface.
5.34.0 · Jul 2026
· source
· release history
Adds StackIT (German sovereign cloud) as a new provider, authenticating via service account key file (--stackit-service-account-key-path) or inline JSON (--stackit-service-account-key) for CI/CD pipelines.
5.29.0 · Jun 2026
· source
· release history
example
Scan a StackIT environment in CI/CD by passing the service account key as inline JSON from a secret manager.$ prowler stackit --stackit-service-account-key '{"type":"serviceAccountKey","key":"..."}'
5.29.0 · Jun 2026
· source
+Compliance WatchlistshippedLets teams pin compliance frameworks from any compliance view, filter to pinned frameworks only, and surface their scores on the Overview page.3 releases · 1 other source · first seen Jan 2026▸
release
Adds Compliance Watchlist feature to pin frameworks and filter views in Prowler Cloud/Private Cloud
5.38.0 · Aug 2026
· source
· release history
Compliance Watchlist (Prowler Cloud/Private Cloud) lets teams pin frameworks from any compliance view, filter the Compliance section to pinned frameworks only, and see pinned framework scores on the Overview page.
5.38.0 · Aug 2026
· source
· release history
New Compliance Watchlist component on the Overview page and /api/v1/overviews/compliance-watchlist API endpoint for monitoring critical compliance frameworks at a glance.
5.17.0 · Jan 2026
· source
· release history
docs
August 6, 2026 Compliance Watchlist Compliance Watchlist keeps the frameworks an organization tracks in one shared list. Pin frameworks from any compliance view, manage several at once through a searchable catalog, and filter the Compliance section to show only the pinned frameworks.
docs update · Aug 2026
· source
+Database connection observabilityshippedLabels Postgres connections with a configurable application name and component alias for per-component attribution in pg_stat_activity.3 releases · 1 other source · first seen Apr 2024▸
release
Compliance overview ingest now runs in a single transaction per scan with a configurable DJANGO_COMPLIANCE_COPY_BATCH_SIZE (default 2000), reducing database write pressure at scale.
5.36.0 · Jul 2026
· source
· release history
Postgres connections are now labeled with application_name="<component>:<alias>" (set via DJANGO_APP_COMPONENT) for per-component attribution in pg_stat_activity.
5.30.0 · Jun 2026
· source
· release history
Labels Postgres connections with application_name="<component>:<alias>" (configurable via DJANGO_APP_COMPONENT) for per-component attributability in pg_stat_activity.
5.30.0 · Jun 2026
· source
· release history
+AWS post-quantum cryptography readiness checksshippedChecks CloudFront, API Gateway, Transfer Server, ACM Private CA, and IAM Roles Anywhere for post-quantum cryptography readiness in TLS, SSH, and PKI configurations.3 releases · 1 other source · first seen Jun 2026▸
release
New AWS check elbv2_listener_pqc_tls_enabled: verifies ELBv2 HTTPS/TLS listeners use post-quantum TLS security policies (TLS 1.2+) to reduce harvest-now-decrypt-later exposure.
5.34.0 · Jul 2026
· source
· release history
New AWS post-quantum cryptography checks: cloudfront_distributions_pqc_tls_enabled, apigateway_domain_name_pqc_tls_enabled, transfer_server_pqc_ssh_kex_enabled, acmpca_certificate_authority_pqc_key_algorithm (new acmpca service), and rolesanywhere_trust_anchor_pqc_pki (new rolesanywhere service).
5.31.0 · Jun 2026
· source
· release history
New AWS post-quantum cryptography readiness checks: cloudfront_distributions_pqc_tls_enabled, apigateway_domain_name_pqc_tls_enabled, transfer_server_pqc_ssh_kex_enabled, acmpca_certificate_authority_pqc_key_algorithm (new acmpca service), and rolesanywhere_trust_anchor_pqc_pki (new rolesanywhere…
5.31.0 · Jun 2026
· source
· release history
example
Run all post-quantum cryptography readiness checks against your AWS environment to identify gaps before the quantum migration deadline.$ prowler aws --checks cloudfront_distributions_pqc_tls_enabled apigateway_domain_name_pqc_tls_enabled transfer_server_pqc_ssh_kex_enabled acmpca_certificate_authority_pqc_key_algorithm…
5.31.0 · Jun 2026
· source
+Azure resource group scoped scanningshippedScopes Azure assessments to one or more resource groups instead of the entire subscription using CLI flags.2 releases · 2 other sources · first seen Jul 2026▸
Also counts toward: Command-line interface
release
Azure scans now support --azure-resource-group / --azure-resource-groups to scope assessments to one or more resource groups instead of the entire subscription.
5.32.0 · Jul 2026
· source
· release history
Adds --azure-resource-group / --azure-resource-groups option to scope Azure scans to one or more resource groups instead of all resources in a subscription.
5.32.0 · Jul 2026
· source
· release history
example
Scope an Azure assessment to specific teams' resource groups to cut scan time and limit result scope during a targeted review.$ prowler azure --az-cli-auth --azure-resource-group rg-prod1 rg-prod2
5.32.0 · Jul 2026
· source
Scope an Azure scan to production resource groups only, avoiding noise from dev/test environments.$ prowler azure --az-cli-auth --azure-resource-group rg-prod1 rg-prod2
5.32.0 · Jul 2026
· source
+M365 Exchange and Entra directory checksshippedChecks M365 Exchange mailbox SMTP domain configuration and Entra directory sync object takeover blocking.3 releases · 1 other source · first seen Mar 2025▸
release
New M365 check exchange_mailbox_primary_smtp_custom_domain verifies mailbox primary SMTP addresses use a custom domain.
5.30.0 · Jun 2026
· source
· release history
New M365 check exchange_mailbox_primary_smtp_custom_domain verifies mailbox primary SMTP addresses use a custom domain.
5.30.0 · Jun 2026
· source
· release history
Adds new Entra check entra_policy_ensure_default_user_cannot_create_tenants for Microsoft 365.
5.4.0 · Mar 2025
· source
· release history
example
Check whether default users in Entra are blocked from creating new tenants.$ prowler microsoft365 --check entra_policy_ensure_default_user_cannot_create_tenants
5.4.0 · Mar 2025
· source
+Enhanced remediation referencesshippedLinks CVE and IaC findings directly to external sources like CVE.org, Prowler Hub, and GitHub Security Advisories.4 releases · first seen Sep 2025▸
release
Container image CVE findings and IaC findings now link remediation references directly to CVE.org, Prowler Hub, and GitHub Security Advisories; Trivy-sourced findings also link correctly into Prowler Hub.
5.26.0 · May 2026
· source
· release history
Adds Prowler Hub menu item and Markdown/AdditionalURLs support in the findings detail UI.
5.13.0 · Oct 2025
· source
· release history
UI: Markdown rendering added to the finding details page.
5.12.0 · Sep 2025
· source
· release history
Adds AdditionalURLs field to CheckMetadata for surfacing additional reference URLs on checks.
5.12.0 · Sep 2025
· source
· release history
+Local platform deploymentshippedEnables running the full Prowler platform locally via Docker Compose without cloud dependency.3 releases · 1 other source · first seen Dec 2024▸
Also counts toward: Kubernetes-native deployment, REST API, Self-hosted deployment, Web management console
release
New VALKEY_SCHEME, VALKEY_USERNAME, and VALKEY_PASSWORD environment variables to configure Celery broker TLS/auth for Valkey/ElastiCache.
5.23.0 · Apr 2026
· source
· release history
Official community-maintained Helm chart published as an OCI artifact to oci://ghcr.io/prowler-cloud/charts/prowler for self-hosted Kubernetes deployments.
5.20.0 · Mar 2026
· source
· release history
Full platform now deployable on-premises via docker compose up -d, serving the UI at https://localhost:3000.
5.0.0 · Dec 2024
· source
· release history
example
Stand up the full Prowler platform locally — UI, API, and persistent storage — without any cloud dependency.$ docker compose up -d
5.0.0 · Dec 2024
· source
+Threat detection checksshippedsuggestedAdds CloudTrail-based detection for privilege escalation, enumeration, and LLM-specific threats like LLMJacking.4 releases · first seen Nov 2024▸
Suggested capability: Security event correlation. This is our guess, not confirmed.
release
Adds new apim_threat_detection_llm_jacking check for Azure API Management, monitoring 25+ LLM API endpoints across major AI providers.
5.11.0 · Aug 2025
· source
· release history
Adds Resource Explorer v2 API actions to the cloudtrail_threat_detection_enumeration check for broader enumeration detection.
5.11.0 · Aug 2025
· source
· release history
Adds 5 new AWS Bedrock checks to detect LLMJacking threats: bedrock_model_invocation_logging_enabled, cloudtrail_threat_detection_llm_jacking, bedrock_agent_guardrail_enabled, bedrock_guardrail_prompt_attack_filter_enabled, and bedrock_guardrail_sensitive_information_filter_enabled.
4.5.0 · Nov 2024
· source
· release history
Adds CloudTrail-based threat detection checks for enumeration and privilege escalation: cloudtrail_threat_detection_enumeration and cloudtrail_threat_detection_privilege_escalation.
4.5.0 · Nov 2024
· source
· release history
+Auto-remediation fixersshippedAdds automated fixes for DocumentDB, EC2, KMS, Neptune, and RDS misconfigurations.2 releases · 2 other sources · first seen Nov 2024▸
Also counts toward: Command-line interface
release
Adds 30 new AWS auto-fixers for Lambda, SQS, ECR, Glacier, OpenSearch, S3, EC2, CloudTrail, and CodeArtifact — run with --fixer to automatically remediate public-exposure misconfigurations.
5.1.0 · Jan 2025
· source
· release history
Adds 6 new auto-remediation fixers for DocumentDB, EC2, KMS, Neptune, and RDS misconfigurations (run with --fixer flag).
4.6.0 · Nov 2024
· source
· release history
example
List every available auto-fixer before running remediation to audit what will be changed.$ prowler aws --list-fixers
5.1.0 · Jan 2025
· source
Auto-remediate publicly exposed EC2 SSH ports across your AWS account in one pass.$ prowler aws --check ec2_instance_port_ssh_exposed_to_internet --fixer
5.1.0 · Jan 2025
· source
+Configurable scan exit codesshippedProvides command-line flags to control the exit code behavior, such as distinguishing between general failures and specific check failures.2 releases · 2 other sources · first seen Nov 2021▸
Also counts toward: CI/CD pipeline integration, Command-line interface
release
Adds -z flag to define the exit code returned when Prowler finds failed checks.
3.2.0 · Feb 2023
· source
· release history
-Z flag controls if Prowler returns exit code 3 on a failed check.
2.6.0 · Nov 2021
· source
· release history
example
Configure ECR vulnerability scanning to only fail when severities meet a specific threshold$ ecr_repository_vulnerability_minimum_severity: 'HIGH'
3.9.0 · Aug 2023
· source
Set a custom exit code (e.g., 3) when Prowler detects failed findings to integrate with CI/CD status checks.$ prowler aws -z 3
3.2.0 · Feb 2023
· source
+Framework ID migrationshippedReplaces FedRAMP 20x Phase One pilot framework IDs with the canonical 'fedramp_20x_ksi_2026' identifier across all tooling.3 releases · first seen Sep 2026▸
release
Automation or stored results referencing pilot framework IDs must be updated to fedramp_20x_ksi_2026
5.43.0 · Sep 2026
· source
· release history
The pilot framework IDs fedramp_20x_ksi_low_aws, fedramp_20x_ksi_low_azure, and fedramp_20x_ksi_low_gcp are replaced by fedramp_20x_ksi_2026; any automation or stored results referencing the pilot IDs must be updated.
5.43.0 · Sep 2026
· source
· release history
FedRAMP 20x Phase One pilot frameworks fedramp_20x_ksi_low_aws, fedramp_20x_ksi_low_azure and fedramp_20x_ksi_low_gcp are replaced by fedramp_20x_ksi_2026
5.43.0 · Sep 2026
· source
· release history
+GCP Organization guided onboardingshippedProvides a guided flow in Prowler Cloud to onboard a GCP Organization by selecting folders and projects from a hierarchy tree and registering each project as a provider.3 releases · first seen May 2025▸
release
Adds UI_SELF_REGISTRATION_ENABLED environment variable for Prowler Private Cloud deployments; set to false to make sign-up invitation-only, hiding the Sign up link and Create organization option.
5.43.0 · Sep 2026
· source
· release history
GCP Organization onboarding in Prowler Cloud is now a single guided flow: provide an org-level credential, select folders and projects from a hierarchy tree, set aliases, test the connection, and register each project as a provider.
5.37.0 · Aug 2026
· source
· release history
Supports CLOUDSDK_AUTH_ACCESS_TOKEN environment variable for GCP authentication.
5.6.0 · May 2025
· source
· release history
+Self-healing background task recoveryshippedAutomatically resumes safe-to-retry background tasks after worker crashes, with manual recovery via a management command, while protecting scan tasks from blind re-runs.3 releases · first seen Jun 2026▸
Also counts toward: Command-line interface
release
Image provider authentication now falls back to Basic when a registry rejects a bearer token, and upgrades to bearer when the server responds with a Bearer challenge to a Basic or anonymous request.
5.41.0 · Sep 2026
· source
· release history
Enables opt-in self-healing background task recovery via DJANGO_TASK_RECOVERY_ENABLED; safe-to-retry tasks (report summaries, cleanups) auto-resume after worker crashes while scan tasks are never blindly re-run.
5.30.0 · Jun 2026
· source
· release history
Adds reconcile_orphan_tasks Django management command for on-demand recovery of orphaned background tasks.
5.30.0 · Jun 2026
· source
· release history
+Azure Management Group onboardingshippedOnboards all Azure subscriptions under a tenant at once in Prowler Cloud using a single tenant-wide service principal.2 releases · 1 other source · first seen Aug 2026▸
release
Adds Azure Management Group onboarding in Prowler Cloud: onboard all subscriptions under a tenant at once by entering the Microsoft Entra tenant ID and authenticating with a single tenant-wide service principal (Cloud/Private Cloud only).
5.39.0 · Aug 2026
· source
· release history
Adds Azure Management Group onboarding via the Prowler Cloud add-provider wizard, allowing single-step discovery and onboarding of all subscriptions under a tenant root management group
5.39.0 · Aug 2026
· source
· release history
docs
- [Azure Management Groups](https://docs.prowler.com/user-guide/tutorials/prowler-cloud-azure-management-groups.md): Discover the Azure subscriptions in your management groups and onboard the ones you select through a single guided wizard
docs update · Aug 2026
· source
+Supply chain integrity for container buildsshippedVerifies checksums of downloaded binaries during container builds and publishes per-architecture SBOMs and build-provenance attestations for API, UI, SDK, and MCP images.3 releases · first seen Aug 2026▸
release
API and SDK container builds now verify checksums of downloaded PowerShell, Trivy, and zizmor binaries before installation.
5.38.0 · Aug 2026
· source
· release history
Container images now publish per-architecture SBOMs and build-provenance attestations as OCI artifacts
5.38.0 · Aug 2026
· source
· release history
Prowler API, UI, SDK, and MCP container images now publish per-architecture SBOMs and build-provenance attestations as OCI attestations.
5.38.0 · Aug 2026
· source
· release history
+Cross-provider compliance rollup viewshippedRolls up the most recent scan of every compatible provider into a single compliance posture per framework, with a per-provider breakdown and a combined executive PDF export.3 releases · first seen Jul 2026▸
release
Compliance view in Prowler Cloud now groups frameworks across all providers of the same type, rolling up into a consolidated posture with per-provider breakdown, findings drill-down, and combined executive PDF report; tabs are renamed to Single Scan and Multiple Scans, with Multiple Scans as the new default.
5.37.0 · Aug 2026
· source
· release history
New Cross-Provider Compliance view (Prowler Cloud/Private Cloud): aggregates the most recent scan of every compatible provider into a single compliance posture per framework with per-provider breakdown and combined PDF export; supports CIS Controls 8.1, CSA CCM 4.0, and DORA 2022/2554.
5.34.0 · Jul 2026
· source
· release history
New Cross-Provider Compliance view (Prowler Cloud/Private Cloud): rolls up the most recent scan of every compatible provider into a single compliance posture per framework (CIS Controls 8.1, CSA CCM 4.0, DORA 2022/2554) with per-provider breakdown and combined executive PDF export.
5.34.0 · Jul 2026
· source
· release history
+StackIT object storage checksshippedsuggestedChecks StackIT object storage buckets for WORM protection, default retention enforcement, and access key expiration.3 releases · first seen Jun 2026▸
Suggested capability: Data access governance. This is our guess, not confirmed.
release
New STACKIT check iaas_server_public_ip_attached: flags IaaS servers with a public IP address directly attached to a network interface.
5.34.0 · Jul 2026
· source
· release history
New StackIT objectstorage service adds three checks: objectstorage_bucket_object_lock_enabled (WORM protection), objectstorage_bucket_retention_policy (default retention enforcement), and objectstorage_access_key_expiration (credential expiry).
5.30.0 · Jun 2026
· source
· release history
New StackIT objectstorage service with three checks: Object Lock (WORM protection), retention policy enforcement, and access key expiration.
5.30.0 · Jun 2026
· source
· release history
+Advanced triage workflow managementshippedManages the full lifecycle of findings through stages such as Open, Remediating, and Risk Accepted with notes and muting capabilities.3 releases · first seen Mar 2025▸
release
Adds findings triage workflow in Prowler Cloud/Enterprise: move findings through Open → Under Review → Remediating → Risk Accepted → False Positive → Resolved, with triage notes and muting; status auto-updates to Resolved or Reopened across scans.
5.32.0 · Jul 2026
· source
· release history
Adds a Status column to the findings table in the Compliance Detail view.
5.9.0 · Jul 2025
· source
· release history
Status extended field added to finding details in the UI.
5.4.0 · Mar 2025
· source
· release history
+Okta API request throttlingshippedConfigures per-second request rate and maximum retry attempts for Okta provider scans to avoid rate-limit errors on large tenants.2 releases · 1 other source · first seen Jul 2026▸
release
Okta provider adds configurable API request throttling (--okta-requests-per-second, default 4 req/s) and retry cap (--okta-retries-max-attempts, default 5) to survive rate limits on large tenant scans.
5.32.0 · Jul 2026
· source
· release history
Adds Okta API request throttling and retry controls: okta_requests_per_second / --okta-requests-per-second (default 4 req/s) and okta_max_retries / --okta-retries-max-attempts (default 5) to keep large Okta scans under rate limits.
5.32.0 · Jul 2026
· source
· release history
example
Prevent Okta rate-limit errors on large tenants by capping request rate and bounding retries.$ prowler okta --okta-requests-per-second 2 --okta-retries-max-attempts 10
5.32.0 · Jul 2026
· source
+Linode (Akamai Cloud) provider scanningshippedScans Linode accounts for misconfigurations across administration, compute, and networking services.2 releases · 1 other source · first seen Jun 2026▸
release
New linode provider: scans Linode (Akamai Cloud) administration, compute, and networking services via prowler linode.
5.31.0 · Jun 2026
· source
· release history
New provider: Scans Linode (Akamai Cloud) covering administration, compute, and networking services.
5.31.0 · Jun 2026
· source
· release history
example
Scan a Linode account for security misconfigurations across administration, compute, and networking services.$ prowler linode
5.31.0 · Jun 2026
· source
+Multi-cloud threat detection expansionshippedAdds dedicated security checks for GitHub organizations and repositories, including ruleset evaluation, immutable release enforcement, and public exposure scanning.3 releases · first seen Aug 2025▸
Also counts toward: Command-line interface
release
New --repo-list-file CLI flag for the GitHub provider loads repositories from a file instead of enumerating them inline.
5.25.0 · Apr 2026
· source
· release history
New GitHub check repository_immutable_releases_enabled detects repositories without immutable releases enforced.
5.15.0 · Dec 2025
· source
· release history
Adds GitHub as a supported cloud provider, enabling security posture assessment of GitHub organizations and repositories via Personal Access Tokens, OAuth App Tokens, or GitHub Apps.
5.10.0 · Aug 2025
· source
· release history
+Extended scan output fieldsshippedsuggestedExpands CSV and HTML report outputs with additional metadata fields including risk ratings, remediation steps, documentation links, and CAF epic mappings.3 releases · first seen Apr 2021▸
Suggested capability: Log enrichment. This is our guess, not confirmed.
Also counts toward: CSV data export
release
Sensitive CLI flag values (tokens, keys, passwords) are now redacted in HTML output Parameters used field.
5.23.0 · Apr 2026
· source
· release history
AWS Organizations findings now include Organizational Unit ID and name across ASFF, OCSF, and CSV output formats.
5.20.0 · Mar 2026
· source
· release history
Adds new CSV/HTML output fields: CHECK_RISK, CHECK_REMEDIATION, CHECK_DOC, CHECK_CAF_EPIC
2.4.0 · Apr 2021
· source
· release history
+OpenStack provider scanningshippedAssesses OpenStack private cloud environments for security misconfigurations across compute and object storage services.3 releases · first seen Feb 2026▸
Also counts toward: Command-line interface
release
Adds 7 new OpenStack Object Storage security checks covering container access control, versioning, encryption, metadata hygiene, and lifecycle management.
5.20.0 · Mar 2026
· source
· release history
Adds 26 new OpenStack security checks across Compute, Networking, Block Storage, and Image services.
5.19.0 · Mar 2026
· source
· release history
Adds OpenStack as a new cloud provider (CLI only) with initial Compute service coverage and first security check, enabling private cloud assessments.
5.18.0 · Feb 2026
· source
· release history
+Cloudflare provider scanningshippedScans Cloudflare infrastructure for misconfigurations across zones, DNS, email security, WAF, bot protection, and TLS/SSL configuration.3 releases · first seen Jan 2026▸
Also counts toward: Command-line interface, Scripting API
release
Cloudflare provider now has full Prowler App (UI) support with 29 security checks covering TLS/SSL, DNS, email security, WAF, bot protection, and zone configuration.
5.19.0 · Mar 2026
· source
· release history
Cloudflare provider credentials now accepted as constructor parameters (api_token, api_key, api_email) for SDK usage.
5.18.0 · Feb 2026
· source
· release history
New Cloudflare provider (CLI) enables scanning of Cloudflare infrastructure for misconfigurations across zones, DNS, email security (SPF, DKIM, DMARC), WAF, bot protection, and TLS/SSL configuration.
5.17.0 · Jan 2026
· source
· release history
+MongoDB Atlas provider scanningshippedProvides assessment of MongoDB Atlas managed database clusters covering encryption, TLS, MFA, auditing, and internet exposure controls.3 releases · first seen Sep 2025▸
release
Adds MongoDB Atlas provider support in the Prowler App for assessing managed database cluster security posture.
5.15.0 · Dec 2025
· source
· release history
Adds MongoDB Atlas as a new provider (API only) with 10 available checks.
5.14.0 · Nov 2025
· source
· release history
New MongoDB Atlas provider (Beta) with 10 security checks covering clusters, projects, and organizations — including TLS, encryption-at-rest, MFA, auditing, and internet-exposure checks.
5.12.0 · Sep 2025
· source
· release history
+AI-assisted check creationshippedProvides AI-driven control generation to automatically create new detection checks and remediations.2 releases · 1 other source · first seen Dec 2024▸
release
New prowler llm provider for AI/LLM red team security testing via promptfoo, covering OWASP LLM Top 10, MITRE ATLAS, and NIST AI RMF with 5000+ test cases (CLI).
5.13.0 · Oct 2025
· source
· release history
AI-driven control creation automatically generates new detection checks and remediations.
5.0.0 · Dec 2024
· source
· release history
example
Run a comprehensive LLM red team evaluation (OWASP LLM Top 10, MITRE ATLAS, NIST AI RMF) against an AI/LLM target.$ npm install -g promptfoo && prowler llm
5.13.0 · Oct 2025
· source
+Guided provider onboarding experienceshippedWalks users through connecting their first cloud provider with contextual empty states and step-by-step prompts.2 releases · first seen Jun 2026▸
release
Prowler's add-provider wizard now connects every provider — AWS, Azure, GCP, Microsoft 365, GitHub, Alibaba Cloud, and Cloudflare — in one step, with teammate invitations available for all providers and Lighthouse AI assistance beside the wizard.
5.47.0 · Oct 2026
· source
· release history
Guided onboarding experience in Prowler Cloud with contextual empty states and first-provider prompts.
5.31.0 · Jun 2026
· source
· release history
+Cloud provider retry configurationverifiedConfigures retry behavior for cloud provider API calls to handle transient errors and rate limits during scanning.1 release · 1 other source · first seen Aug 2025▸
Also counts toward: Command-line interface
release
Adds GCP provider retry configuration support.
5.10.0 · Aug 2025
· source
· release history
command line
--aws-read-timeout — Seconds to wait for a response from an AWS endpoint before retrying (Default: 60)
5.42.0 · Sep 2026
· command-line history
+Manual finding triage and resolutionshippedAdds a Resolved triage status for manual findings, recording written evidence and treating the finding as an effective PASS for 90 days or until a real failure is detected.2 releases · first seen Aug 2026▸
release
Adds new MANUAL finding triability as PASS with evidence collection, author tracking, and automatic expiration after 90 days or upon re-failure
5.39.0 · Aug 2026
· source
· release history
Adds Resolved triage status for MANUAL findings in Prowler Cloud, recording written evidence and verifying the finding as an effective PASS for 90 days or until a real failure is detected (Cloud/Private Cloud only).
5.39.0 · Aug 2026
· source
· release history
+AWS Nitro Enclaves security checksshippedChecks EC2 instances and KMS keys used with Nitro Enclaves for hygiene controls including IMDSv2, public IP exposure, ingress rules, vsock proxy ports, and KMS attestation policy correctness.2 releases · first seen Aug 2026▸
release
Adds 11 new passive ec2_confidential_workload_host_* and kms_key_enclave_* checks for AWS Nitro Enclaves confidential computing.
5.37.0 · Aug 2026
· source
· release history
Adds 11 new AWS Nitro Enclaves CSPM checks: five ec2_confidential_workload_host_* checks for parent-instance hygiene (IMDSv2, public IP, ingress, vsock proxy ports, host state) and six kms_key_enclave_* checks for KMS attestation-policy correctness, mapped across 23 compliance frameworks including NIST 800-53 Rev…
5.37.0 · Aug 2026
· source
· release history
+API Gateway stage variable secret checkshippedsuggestedScans API Gateway REST API stage variables for hardcoded passwords, API keys, and tokens.2 releases · first seen Jul 2026▸
Suggested capability: Sensitive data discovery. This is our guess, not confirmed.
release
New AWS check apigateway_restapi_no_secrets_in_stage_variables: scans API Gateway REST API stage variables for hardcoded passwords, API keys, and tokens.
5.32.0 · Jul 2026
· source
· release history
New AWS check apigateway_restapi_no_secrets_in_stage_variables: scans API Gateway REST API stage variables for hardcoded passwords, API keys, and tokens.
5.32.0 · Jul 2026
· source
· release history
+AWS WAF logging checkshippedFlags AWS WAF Classic Regional Web ACLs that do not have Kinesis Data Firehose logging enabled.2 releases · first seen Jul 2026▸
release
New AWS check waf_regional_webacl_logging_enabled: flags AWS WAF Classic Regional Web ACLs without Kinesis Data Firehose logging.
5.32.0 · Jul 2026
· source
· release history
New AWS check waf_regional_webacl_logging_enabled: detects AWS WAF Classic Regional Web ACLs without logging to a Kinesis Data Firehose stream.
5.32.0 · Jul 2026
· source
· release history
+Okta application hardening checksshippedChecks Okta admin console and dashboard configuration including MFA, session timeout, and network zone enforcement.1 release · 1 other source · first seen Jun 2026▸
release
Adds new application service for the Okta provider with 6 checks covering admin console and dashboard hardening (MFA, phishing-resistant auth, session idle timeout, network zone enforcement).
5.29.0 · Jun 2026
· source
· release history
example
List check categories for provider$ prowler <provider> --list-categories
+Ephemeral resource noise reductionshippedAutomatically zeroes failed findings counts for resources absent from the latest full-scope scan to prevent polluting the Resources page.1 release · 1 other source · first seen May 2026▸
release
Adds scan-reset-ephemeral-resources post-scan API task that zeroes failed_findings_count for resources absent from the latest full-scope scan, preventing ephemeral resources from polluting the Resources page sort.
5.26.0 · May 2026
· source
· release history
example
Launch local security dashboard$ prowler dashboard
+CloudTrail resource timelineshippedsuggestedDisplays the last 90 days of CloudTrail events, actor details, and request/response payloads for specific resources.2 releases · first seen Feb 2026▸
Suggested capability: Log collection. This is our guess, not confirmed.
Also counts toward: REST API
release
Adds AWS Resource Timeline: a new Events tab in Findings and Resource detail cards shows the last 90 days of AWS CloudTrail events with expandable event rows, actor details, request/response JSON payloads, error info, and a read-event toggle.
5.21.0 · Mar 2026
· source
· release history
New GET /api/v1/resources/{id}/events API endpoint retrieves AWS resource modification history from CloudTrail.
5.18.0 · Feb 2026
· source
· release history
+AI/LLM red team security testingshippedEnables automated red team evaluation of AI targets against OWASP LLM Top 10, MITRE ATLAS, and NIST AI RMF using promptfoo-based testing.1 release · 1 other source · first seen Oct 2025▸
release
New prowler llm provider for AI/LLM red team security testing via promptfoo, covering OWASP LLM Top 10, MITRE ATLAS, and NIST AI RMF with 5000+ test cases (CLI).
5.13.0 · Oct 2025
· source
· release history
example
Run a comprehensive LLM red team evaluation (OWASP LLM Top 10, MITRE ATLAS, NIST AI RMF) against an AI/LLM target.$ npm install -g promptfoo && prowler llm
5.13.0 · Oct 2025
· source
+OCI provider onboardingshippedOnboards Oracle Cloud Infrastructure tenancies by selecting a home region to validate credentials and discover subscribed regions.2 other sources · first seen Oct 2025▸
docs
In , note the Home Region identifier (for example, me-abudhabi-1 ). Any other region the tenancy is subscribed to also works. Home Region : select it from the list (for example, me-abudhabi-1 The home region is used only to validate the credentials and discover the regions the tenancy is subscribed to.
seen Oct 2026
· source
example
Scan Oracle Cloud Infrastructure against the CIS 3.0 benchmark after authenticating a local OCI session.$ oci session authenticate && prowler oci
5.13.0 · Oct 2025
· source
+Persistent scan storageshippedEnsures scan reports and findings are retained in persistent storage for always-on accessibility.2 releases · first seen Dec 2024▸
release
Adds new API endpoint to retrieve compliance overviews metadata.
5.5.0 · Apr 2025
· source
· release history
Persistent storage for scan reports ensures findings are retained and always accessible.
5.0.0 · Dec 2024
· source
· release history
+Check allowlist managementshippedEnables the use of DynamoDB tables to store and apply allowlists for filtering out specific findings during scans.2 releases · first seen Jan 2022▸
release
AWS allowlist file includes AWS Control Tower resources for landing zone coverage
3.11.0 · Oct 2023
· source
· release history
Adds extra7164 check for CloudWatch Log Groups KMS protection
2.7.0 · Jan 2022
· source
· release history
+Configurable credential expiration checksshippedDetects and configures thresholds for unused IAM credentials, standardizing checks for access keys and console access.2 releases · first seen Oct 2023▸
release
The max_unused_access_keys_days configuration value allows customizing unused access key age thresholds for IAM checks.
3.10.0 · Oct 2023
· source
· release history
Unused credential detection now defaults to 45 days instead of the previous fixed intervals.
3.10.0 · Oct 2023
· source
· release history
+IAM administrator access detectionshippedsuggestedVerifies if IAM roles or users have administrator access policies attached to identify overly privileged identities.1 release · 1 other source · first seen Oct 2023▸
Suggested capability: Data access governance. This is our guess, not confirmed.
release
prowler aws can now run the new AWS IAM check iam_role_administratoraccess_policy.
3.10.0 · Oct 2023
· source
· release history
example
Run the new IAM check that verifies if an IAM role has administrator access policy attached$ prowler aws --checks iam_role_administratoraccess_policy
3.10.0 · Oct 2023
· source
+Check inventory exportshippedExports all available security checks to a JSON file for inspection or scripting purposes.2 other sources · first seen Aug 2023▸
Also counts toward: JSON data export
example
Export all available Prowler checks to a JSON file for inspection or scripting with --checks-file$ prowler aws --list-checks-json > checks.json
3.9.0 · Aug 2023
· source
List available checks for provider$ prowler <provider> --list-checks
+MFA-enforced session scanningshippedSupports scanning with explicit MFA prompts and ARN codes for IAM entities that enforce multi-factor authentication.1 release · 1 other source · first seen Jun 2023▸
Also counts toward: Command-line interface, Multi-factor authentication
release
Adds the --mfa flag to prowler aws to prompt for MFA ARN and code, enabling session assumption when the IAM entity enforces MFA
3.6.0 · Jun 2023
· source
· release history
example
Run an AWS scan enforcing MFA for the current IAM identity.$ prowler aws --mfa
3.6.0 · Jun 2023
· source
+PostgreSQL findings outputshippedsuggestedSupports sending scan findings directly to a PostgreSQL database via a dedicated connector with environment variable configuration.2 releases · first seen Jul 2022▸
Suggested capability: Log routing. This is our guess, not confirmed.
release
Adds PostgreSQL as an output destination for findings via the new connector
2.11.0 · Jul 2022
· source
· release history
Adds support for environment variables in the PostgreSQL database connector configuration
2.11.0 · Jul 2022
· source
· release history
+AWS provider credential delegation via teammate inviteshippedAllows a user without direct AWS account access to invite a teammate to complete IAM role setup, with Prowler Cloud sending the invite link by email and displaying it in the UI.1 release · 1 other source · first seen Feb 2020▸
release
Native AWS AssumeRole support allows using custom profiles with role assumptions
2.2.0 · Feb 2020
· source
· release history
docs
To delegate the AWS connection, select I don't have access, invite a teammate on the same step when you cannot create the IAM role or do not have the account credentials. Prowler App sends the invitation to the tenant and shows the link to share. Prowler Cloud also emails it.
seen Oct 2026
· source
+Runtime version currency checksshippedsuggestedFlags cloud workloads running outdated or unsupported runtime versions, covering PHP on GCP App Engine and AWS Elastic Beanstalk.1 release · first seen Oct 2026▸
Suggested capability: Vulnerability database matching. This is our guess, not confirmed.
release
Adds new PHP version checks across platforms: a new GCP appengine service with the appengine_version_php_runtime_supported check flagging App Engine serving versions on PHP runtimes without security fixes, the elasticbeanstalk_environment_php_platform_updated check flagging Elastic Beanstalk PHP environments on…
5.46.0 · Oct 2026
· source
· release history
+IAM wildcard marketplace subscribe detectionshippedDetects wildcard aws-marketplace:Subscribe grants in IAM policies to prevent accidental billing incidents.1 release · first seen Apr 2026▸
release
New iam_policy_no_wildcard_marketplace_subscribe and iam_inline_policy_no_wildcard_marketplace_subscribe checks catch wildcard aws-marketplace:Subscribe grants that could turn an IAM misconfiguration into a billing incident.
5.24.0 · Apr 2026
· source
· release history
+Vercel provider scanningshippedsuggestedAudits Vercel deployments, domains, projects, and team settings for security misconfigurations using API token authentication.1 release · first seen Apr 2026▸
Suggested capability: Credentialed vulnerability scanning. This is our guess, not confirmed.
release
New Vercel provider: connect via API token to audit deployments, domains, projects, and team settings with 26 built-in security checks.
5.23.0 · Apr 2026
· source
· release history
+AWS Service Management improvementsshippedEnables editing organization names, running scoped connection tests, and deleting organizational units via the UI.1 release · first seen Mar 2026▸
Also counts toward: Web management console
release
Adds AWS Organizations UI management improvements: edit organization names and credentials, run connection tests scoped to all accounts or a specific organizational unit, and delete individual organizational units or full organizations.
5.21.0 · Mar 2026
· source
· release history
+OpenSearch false positive suppressionshippedsuggestedAllows excluding known trusted IPs from OpenSearch public accessibility checks via configuration.1 release · first seen Mar 2026▸
Suggested capability: Infrastructure-as-code security scanning. This is our guess, not confirmed.
release
New trusted_ips configuration option for opensearch_service_domains_not_publicly_accessible eliminates false positives when an OpenSearch domain restricts access to known IPs via resource policy.
5.20.0 · Mar 2026
· source
· release history
+AI coding assistant integrationshippedProvides an AI Skills Pack following the agentskills.io standard so external AI coding assistants can understand and contribute to the cyber tooling codebase.1 release · first seen Jan 2026▸
release
AI Skills Pack added for Claude Code, OpenCode, and Codex following the agentskills.io standard to help AI coding assistants understand and contribute to Prowler's codebase.
5.17.0 · Jan 2026
· source
· release history
+Azure Entra performance enhancementshippedsuggestedImproves Azure scan performance by requiring AuditLog.Read.All permission on service principals.1 release · first seen Jan 2026▸
Suggested capability: Log collection. This is our guess, not confirmed.
release
Azure service principals used to scan Azure must now be granted the AuditLog.Read.All Microsoft Graph permission due to an additional API call required for the Azure Entra performance enhancement.
5.17.0 · Jan 2026
· source
· release history
+AWS Service WatchlistshippedsuggestedAllows users to pin and monitor specific AWS services or findings as a watchlist for prioritized oversight of critical infrastructure components.1 release · first seen Aug 2025▸
Suggested capability: Log routing. This is our guess, not confirmed.
Also counts toward: S3 export
release
Adds Amazon S3 integration to automatically deliver scan reports to one or more S3 buckets across any provider combination.
5.10.0 · Aug 2025
· source
· release history
+Check execution via aliasshippedEnables executing security checks by their assigned aliases using the check identifier flag, providing an alternative to full check names.1 release · first seen Oct 2023▸
release
Check Aliases via CheckAliases metadata key enable executing checks by alias using -c/--checks
3.11.0 · Oct 2023
· source
· release history
+IAM temporary credential detectionshippedIdentifies IAM users that have active or recently used temporary security credentials to assess session hygiene.1 release · first seen Oct 2023▸
release
New account check account_maintain_different_contact_details_to_security_billing_and_operations
3.11.0 · Oct 2023
· source
· release history
+CloudTrail shadow trail detectionshippedEnsures CloudTrail checks identify and include shadow trails in their results for multi-region and organization-wide scans.1 release · first seen Oct 2022▸
release
CloudTrail checks 21, 22, 23, 24, 26, and 27 now include shadow trails in results for multi-region and AWS organizations
2.12.0 · Oct 2022
· source
· release history
+Async report generationshippedBackgrounds the report generation process during scan execution to prevent blocking standard output and improve CLI responsiveness.1 release · first seen Aug 2021▸
release
Saves reports in the background while displaying standard output when using -M option
2.5.0 · Aug 2021
· source
· release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
View
Source
No command matches.
load a captured run
composed command
No matchesTry a different search, or clear a filter to see more.
option surface across analysed releases
options at that releaseadded, per releaseremoved, per release
option
found in
since
description
No matchesTry a different search, or clear a filter to see more.
option changes per release — drag across the rail to set a range
→
Values are placeholders taken from each option’s declared default.
Nothing is executed here — the output shown is a recording of a run
that already happened.
Screenshots
From the release notes, newest first. Click one to see it full size.
Breaking-change disciplinehow rarely a release breaks users, and notice given
Maintenance riskquiet time against its own cadence, maintainers
Innovation & surfacenew capabilities, API and MCP surface
Community health
Contributor trenddistinct committers, this year against last
Maintainer concentrationbus factor now against a year ago
Issue backlog trendissues closed per issue opened, 12 months
Responsivenessmedian time to a maintainer’s first reply
Nine scores for Prowler, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Each score is 0–100 on a published rubric, derived from data this site already shows.
A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
Documentation quality — the release-notes rubric published on the analytics page, unchanged.
Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Prowler puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Issue, contributor and maintainer activity in toniblyx/prowler, 2023-10 – 2026-09,
as of 2026-09-25. Twelve-month figures first; the trend lines run
the whole window.
Contributors149+74 vs prior 12 months
Maintainers11+6 joined · −6 left, last 12 months
Bus factor6committers behind half the commits
Community-filednot measuredof issues opened, last 12 months
Median time to closenot measuredissues closed, last 12 months
Open backlognot measuredopen issues today
Issues opened / monthnot measured
Open backlognot measured
Contributors / month15
Commits / month88
Stars14,838
Issue themes, last 12 monthsnot measured
Counts from the project's public repository and git history; no individuals
are identified. Maintainers are the committers covering 80% of the last year's
commits. how we measure this
Ships a vulnerable library
What its latest release locks, checked against known advisories.
@modelcontextprotocol/sdk 1.26.0 in its ui image
high
Prowler 5.47.0 builds its ui image from ui/pnpm-lock.yaml, which locks @modelcontextprotocol/sdk 1.26.0. That version has GHSA-22jm-h49p-29qw and 3 other high or critical flaws.
Fixed in @modelcontextprotocol/sdk 1.32.0. No Prowler release includes it yet.
Prowler 5.47.0 builds its ui image from ui/pnpm-lock.yaml, which locks brace-expansion 5.0.9. That version has GHSA-6j4f-fj2g-mc7p and 1 other high or critical flaw.
Fixed in brace-expansion 5.0.11. No Prowler release includes it yet.
Prowler 5.47.0 builds its ui image from ui/pnpm-lock.yaml, which locks fast-uri 3.1.6. That version has GHSA-58mr-gqgx-xq4g and 1 other high or critical flaw.
Fixed in fast-uri 3.1.7. No Prowler release includes it yet.