Security Onion
3.4.0-20261102 open-sourceThe section your link pointed to isn't on Security Onion's page any more, so we've brought you to the top.
Security Onion is a free and open Linux distribution for threat hunting, enterprise security monitoring, and log management.
sudo tcpdump -nni eth1
ls -la /nsm/zeek/logs/current
so-elasticsearch-index-growth
so-elasticsearch-index-growth
so-import-evtx /path/to/logs.evtx
Summary
Security Onion is a free, open-source Linux distribution for network security monitoring, threat hunting, and log management, built around Suricata, Zeek, and the Elastic Stack behind a unified web console. It is deployed as a self-hosted grid on your own hardware or virtual machines, with images also available in AWS, Azure, and GCP marketplaces, and is aimed at SOCSOCA security operations center, the team or function that monitors threats, investigates alerts and coordinates incident response. Its work can be internal, outsourced or shared. analysts and threat hunters rather than individual researchers. A paid Pro tier adds AI-assisted investigation features and enterprise integrations, but the core distribution and its packet capturepacket captureA packet capture, recorded network packets that can be inspected later. Analysts use it to reconstruct communication and investigate protocol behavior or suspicious traffic., IDSIDSAn intrusion detection system, monitoring traffic or host activity for suspicious behavior and producing alerts. Detection alone does not necessarily block the activity., and log analysis tooling remain free. The README frames it as a full monitoring stack rather than a point tool, combining network metadata, full packet capture, and intrusion detection in one platform. Development is active, with over a thousand commits in the past year, 53 contributors, and a release only weeks ago.
Security Onion is a free and open Linux distribution for threat hunting, enterprise security monitoring, and log management.
How Security Onion helps
What is actually crossing the wire between these two hosts right now?
Zeek and Suricata generate network metadata and full packet capture off the live traffic, letting an analyst pull the raw packets behind any flow rather than just a summary of it
Which alerts in this pile of events actually deserve a look?
Suricata-driven IDS detections and host events from Elastic Fleet land in the unified console, with an AI-assisted Assistant able to toggle already-investigated queries out of the triage view
Has this host talked to something it shouldn't have before we noticed?
full packet capture is retained so an analyst can go back and replay or extract the raw session once a suspicious host or indicator is identified after the fact
Are all the nodes in this grid actually running the version and ruleset I think they are?
the console checks Elasticsearch version compatibility across every node in the cluster and flags grid nodes stuck on an outdated version that failed to sync
Did the log source I just onboarded actually get mapped into a usable schema?
the Sigma rules pipeline maps sources like Microsoft 365 and Fortigate logs into the platform's normalized fields so hunts and detections run against them consistently
What happened during this investigation, and can I hand it to someone else?
AI session transcripts and structured session report templates attach directly to the case report, keeping the analyst's reasoning alongside the evidence in one document
Languages
Features
Built from Security Onion's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- Security Onion covers 7 of the 34 network analysis capabilities we track.
- Security Onion covers 1 of the 5 network observation capabilities we track.
What Security Onion offers you
- Air-gapped deployment3
- Command-line interface2
- Offline mode2
- CSV data export1
- JSON data export1
- Role-based access control1
- User-defined detection rules1
- Web management console1
- REST API
No capabilities match.
Rule source management and updates 2 features Network analysis since 2024
Detections module automation shipped Provides automated detection rule updates and configuration management within a dedicated Detections module, supporting both online and air-gapped environments.
Shared capability: Rule source management and updates
Also counts toward: Air-gapped deployment, Offline mode
release
- Adds configurable timeouts, including per-automation turn timeouts and configurable timeouts for detection engine syncs, giving operators more control over automation and sync behaviour. 3.4.0-20261102 · Nov 2026 · source · release history
-
Automatically runs
so-rule-updatewhen rule configuration changes. 2.4.150-20250512 · May 2025 · source · release history -
Add
detections_without_licenseoption to allow detections without a license key 2.4.80-20240624 · Jun 2024 · source · release history -
Add Detection AutoUpdate configenables automatic detection rule updates in the new Detections module 2.4.60-20240320 · Mar 2024 · source · release history -
Airgap Support - Detections moduleallows the Detections module to operate in offline/air-gapped environments 2.4.60-20240320 · Mar 2024 · source · release history
Rule repository identification shipped Adds `RulesetName` fields to rule repositories for improved identification and management.
Shared capability: Rule source management and updates
release
-
Adds
RulesetNameto rule repository configuration. 2.4.170-20250812 · Aug 2025 · source · release history -
Adds
RulesetNamefield to Rule Repos for improved rule repository identification. 2.4.160-20250625 · Jun 2025 · source · release history
Network traffic analysis 2 features Network observation since 2024
Network protocol parsing shipped Breaks down network protocol traffic for analysis, with parsers that can be added or removed to match the environment.
Shared capability: Network traffic analysis
release 10 total
-
The
icsnpp-modbusparser is removed from defaults.yaml; grids relying on the default Modbus protocol parser will no longer have it enabled after upgrade. 3.2.0-20260729 · Jul 2026 · source · release history - Exposes login form lifespan as a configurable setting in the Security Onion Console. 3.0.0-20260331 · Mar 2026 · source · release history
- Exposes login form session lifespan as a configurable option in the Security Onion console. 2.4.210-20260302 · Mar 2026 · source · release history
- Adds NIC channel customization for network interface tuning. 2.4.180-20250916 · Sep 2025 · source · release history
- Upgrades Zeek EtherCAT plugin. 2.4.170-20250812 · Aug 2025 · source · release history
-
Adds support for
dns.resolved_ipECS field in parsing. 2.4.160-20250625 · Jun 2025 · source · release history
Zeek traceroute and NTP integrations shipped Adds support for Zeek traceroute and NTP log integrations to expand network visibility.
Shared capability: Network traffic analysis
release
- Adds Zeek traceroute and NTP log integrations. 2.4.130-20250311 · Mar 2025 · source · release history
Packet capture (live and offline) 1 feature Network analysis since 2025
Distributed grid PCAP handling shipped Supports importing and processing PCAP files from sensors within distributed grid deployments.
Shared capability: Packet capture (live and offline)
release
- Supports PCAP imports for sensors in distributed grid deployments. 2.4.140-20250324 · Mar 2025 · source · release history
Display filtering 1 feature Network analysis since 2025
Detection status visualization shipped Provides specialized views such as hunt views to monitor and filter detection statuses.
Shared capability: Display filtering
release
- Adds filter support in the relevant UI views. 2.4.190-20251024 · Oct 2025 · source · release history
- Adds detection status hunt view. 2.4.120-20250212 · Feb 2025 · source · release history
Capture file formats 1 feature Network analysis since 2023
PCAP analysis shipped Analyses captured packet files so investigators can examine network sessions after the fact.
Shared capability: Capture file formats
release
- Supports multiple capinfos versions for PCAP analysis compatibility. 3.2.0-20260729 · Jul 2026 · source · release history
example
-
Import network capture data into Security Onion for packet analysis.
Navigate to SOC Config > Data Ingestion and select 'PCAP/EVTX Import' to upload .pcap files.2.4.3 · Jul 2023 · source
Intrusion detection and rules 1 feature Network analysis since 2026
Multi-event correlation rules shipped Enables the creation of correlation rules in the detection engine that span multiple events for richer threat detection.
Shared capability: Intrusion detection and rules
Also counts toward: User-defined detection rules
release
- Security Onion now supports initial Correlations, enabling multi-event correlation rules in the detection engine. 3.4.0-20261102 · Nov 2026 · source · release history
Network traffic logging 1 feature Network analysis since 2025
DNS log enrichment shipped Supports the `dns.resolved_ip` field for enriching DNS logs with resolved IP addresses.
Shared capability: Network traffic logging
release
-
Adds Zeek
dns.resolved_ipfield logging. 2.4.180-20250916 · Sep 2025 · source · release history -
Adds
dns.resolved_ipfield support for DNS log enrichment. 2.4.170-20250812 · Aug 2025 · source · release history
TLS inspection and fingerprinting 1 feature Network analysis since 2025
PostgreSQL metrics collection shipped Optionally gathers PostgreSQL metrics when configured to do so.
Shared capability: TLS inspection and fingerprinting
release
- Adds toggleable PostgreSQL metrics collection. 3.2.0-20260729 · Jul 2026 · source · release history
-
Adds JA4D fingerprinting option via
config.zeek.ja4for enhanced TLS client fingerprinting. 2.4.200-20251216 · Dec 2025 · source · release history
example
-
Enable JA4D TLS fingerprinting in Zeek to get richer client classification beyond standard JA4.
In the SOC console, go to Administration > Configuration > zeek > config.zeek.ja4 and enable the JA4D option.2.4.200-20251216 · Dec 2025 · source
Other / not yet classified 45 features Features we have not matched to a capability yet. A suggested match is marked.
Gemma-based AI agents and memory shipped Provides AI-driven agents that can automatically investigate alerts and help craft new detection logic.
previously: Agentic AI workflows
release 21 total
-
Security Onion Pro now includes Agentic AI Automations, enabling automated AI-driven workflows within the platform.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
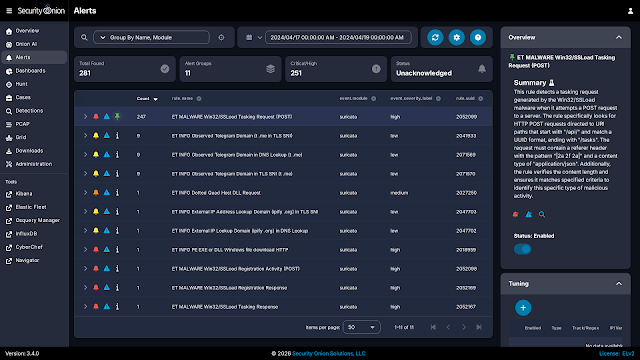 announced · Nov 2026
· source
· release history
- Raise the SOAI Sonnet default small context limit to 1 million tokens. 3.4.0-20261102 · Nov 2026 · source · release history
-
Adds Onion AI Reports Tools (Pro feature).
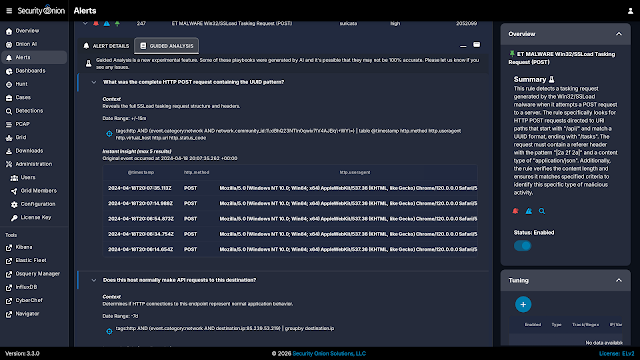 announced · Sep 2026
· source
· release history
- Introduces Agent Studio with agentic memory for Pro users. announced · Sep 2026 · source · release history
-
The Detection Engineer agent configuration key is renamed to
DetectionEngineer; existing configurations using the old key will need to be updated. 3.2.0-20260729 · Jul 2026 · source · release history - Investigator and Engineer roles can now leverage Gemma LLM capabilities 3.2.0-20260729 · Jul 2026 · source · release history
Elasticsearch index management shipped Manages Elasticsearch indices, data stream lifecycles, and cluster health to keep stored data organised and accessible.
release 15 total
-
Adds ES Troubleshoot capability accessible from the Grid Screen.
announced · Sep 2026
· source
· release history
- Adds data stream lifecycle management support for Elasticsearch index management. 3.2.0-20260729 · Jul 2026 · source · release history
- Upgrades to Elasticsearch 9.3.7. 3.2.0-20260729 · Jul 2026 · source · release history
- Adds cluster health monitoring option to telegraf.conf for Elasticsearch observability. 3.2.0-20260729 · Jul 2026 · source · release history
- Removes Stenographer (steno); PCAP capture and cleanup now handled by Suricata. 3.0.0-20260331 · Mar 2026 · source · release history
- Stenographer (steno) is removed; any configuration or workflows depending on Stenographer for PCAP capture will break — PCAP is now handled by Suricata. 3.0.0-20260331 · Mar 2026 · source · release history
example
-
Import EVTX files directly from the command line for forensics or analysis.
so-import-evtx /path/to/logs.evtx2.4.3 · Jul 2023 · source
Configuration file support verified Accepts a custom configuration file so users can override default settings for their environment.
Also counts toward: Command-line interface
release 8 total
-
Add
openai_embeddingsto the YAML configuration to enable OpenAI embedding support.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ 3.4.0-20261102 · Nov 2026 · source · release history -
Adds
cluster_healthoption totelegraf.conffor metrics control 3.2.0-20260729 · Jul 2026 · source · release history -
base_urlis no longer a standalone configuration field; it must now be defined within the certificate Subject Alternative Name (SAN) list. 2.4.10-20230815 · Aug 2023 · source · release history -
Move
base_urlconfiguration into the certificate Subject Alternative Name (SAN) via PR #11002 2.4.10-20230815 · Aug 2023 · source · release history - Adds Quicklinks to common configs in the UI. 2.4.2 · Jun 2023 · source · release history
- Adds capability to Allow for any docker container to have extra hosts and custom binds via configuration. 2.4.2 · Jun 2023 · source · release history
command line
-
--config — optional config file to use instead of the default config file2.3.280-20231128 · Nov 2023 · command-line history
Upgrade and hotfix resumability shipped Lets administrators resume a failed upgrade or hotfix from where it stopped rather than starting over.
release 8 total
-
Adds an x86-64-v3 CPU pre-flight check to
soupto catch incompatible hardware before an upgrade proceeds.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ 3.3.0-20260911 · Sep 2026 · source · release history - Allows airgap installs to reuse previously extracted Docker images, reducing re-extraction time. 3.3.0-20260908 · Sep 2026 · source · release history
- Detects hand-placed local/salt files during Auto State Apply to surface conflicts before they break state runs. 3.3.0-20260908 · Sep 2026 · source · release history
- Makes failed soup upgrades and hotfixes resumable instead of requiring a full restart. 3.2.0-20260729 · Jul 2026 · source · release history
- Verifies Elasticsearch version compatibility across all nodes in the cluster. 3.1.0-20260521 · May 2026 · source · release history
- Adds upgrade path support from 2.4.x to Security Onion 3.0. 3.0.0-20260331 · Mar 2026 · source · release history
Sigma rule support shipped suggested Runs Sigma rules against endpoint logs, including in environments with no internet access.
Suggested capability: Intrusion detection and rules. This is our guess, not confirmed.
Also counts toward: Air-gapped deployment
release
- Sigma pipelines are now stored in a managed directory for cleaner rule organisation. 3.4.0-20261102 · Nov 2026 · source · release history
- Supports Sigma playbooks (including airgap environments), enabling SigmaHQ rules against Elastic Defend logs. 3.2.0-20260729 · Jul 2026 · source · release history
- Adds per-OS-type process creation (proc_creation) Sigma rule handling. 3.1.0-20260521 · May 2026 · source · release history
- Provides more flexibility for AutoEnable Sigma rules. 2.4.120-20250212 · Feb 2025 · source · release history
- Supports regex in Suricata rule management within the Detections interface. 2.4.90-20240729 · Jul 2024 · source · release history
- Auto-enabled Sigma rules based on user role or default configuration 2.4.70-20240529 · May 2024 · source · release history
Elasticsearch index growth monitoring shipped Provides commands and metrics to monitor Elasticsearch index growth trends and identify storage consumers.
Also counts toward: Command-line interface
release
- Upgrades Elasticsearch to 9.4.5. 3.3.0-20260908 · Sep 2026 · source · release history
-
Adds
so-elasticsearch-index-growthcommand for monitoring Elasticsearch index growth. 2.4.170-20250812 · Aug 2025 · source · release history -
Adds
so-elasticsearch-index-growthcommand to monitor Elasticsearch index growth trends. 2.4.160-20250625 · Jun 2025 · source · release history - Collects Elasticsearch index sizes as a new storage metric. 2.4.150-20250512 · May 2025 · source · release history
example
-
Monitor Elasticsearch index growth to identify storage pressure before running out of disk space.
so-elasticsearch-index-growth2.4.170-20250812 · Aug 2025 · source -
Check Elasticsearch index growth to identify data sources consuming storage faster than expected.
so-elasticsearch-index-growth2.4.160-20250625 · Jun 2025 · source
Custom pipeline management shipped Enables deployment and management of custom Elasticsearch and Logstash pipelines through the web interface.
Also counts toward: Web management console
release
-
Expose
log.levelandlog.formatconfiguration keys in SOC for Logstash pipeline control 3.3.0-20260908 · Sep 2026 · source · release history - Adds a local custom Logstash pipeline template support. 2.4.120-20250212 · Feb 2025 · source · release history
- Adds HTTP/2 support to the Elastic Agent Logstash pipeline. 2.4.120-20250212 · Feb 2025 · source · release history
- Manage custom Elasticsearch and Logstash pipelines via the UI 2.4.50-20240220 · Feb 2024 · source · release history
example
-
Deploy and manage custom pipeline configurations directly through the web interface.
In the Security Onion UI, navigate to the Pipelines section to add or edit Elasticsearch/Logstash pipelines.2.4.50-20240220 · Feb 2024 · source
Elastic Defend integration management shipped Allows the tool to manage Elastic Defend policies on endpoints, including installing the integration and enabling CommunityID logging for enhanced visibility.
release
- Switches Elastic Agent log ingestion from the deprecated logs integration to filestream. 3.0.0-20260331 · Mar 2026 · source · release history
- The Elastic Agent logs integration is replaced by filestream; any custom configurations using the deprecated logs integration will need to migrate to filestream. 3.0.0-20260331 · Mar 2026 · source · release history
- Adds initial support for managing Elastic Defend Filters through Security Onion. 2.4.110-20241004 · Oct 2024 · source · release history
- Enables CommunityID for Elastic Defend Logs 2.4.5 · Aug 2023 · source · release history
- Adds Elastic Defend Integration on Endpoints Policy to manage endpoint protection via the platform. 2.4.2 · Jun 2023 · source · release history
Playbook automation support shipped Enables the creation and execution of automated response workflows with dedicated configuration parsing and airgap compatibility.
Also counts toward: Air-gapped deployment, Offline mode
release
- Adds configurable timeouts, including per-automation turn timeouts and configurable timeouts for detection engine syncs, giving operators more control over automation and sync behaviour. 3.4.0-20261102 · Nov 2026 · source · release history
- Adds Playbooks feature with support for airgap environments and configurable ruleset repos. 2.4.170-20250812 · Aug 2025 · source · release history
- Adds Playbooks feature with a dedicated repo config and parsing support for automated response workflows. 2.4.160-20250625 · Jun 2025 · source · release history
- Adds airgap support for Playbooks, enabling Playbook functionality in isolated/offline deployments. 2.4.160-20250625 · Jun 2025 · source · release history
Grid node scaling and specialization shipped Supports the deployment and configuration of specialized grid nodes, including Dedicated Fleet Nodes for traffic separation and Heavy Nodes for increased processing capacity.
release
- Renames forward node to sensor node throughout the platform. 2.4.200-20251216 · Dec 2025 · source · release history
- Adds additional Fleet Node state visibility in the UI. 2.4.180-20250916 · Sep 2025 · source · release history
- Adds support for Heavy Nodes in the grid architecture 2.4.5 · Aug 2023 · source · release history
- Adds Dedicated Elastic Fleet Node role for separating fleet management traffic. 2.4.2 · Jun 2023 · source · release history
Output and index control verified Exposes command-line options to control where output is sent and which index is used during a run.
release
- Add time zone selection to Grid page 2.4.3 · Jul 2023 · source · release history
command line
-
--index2.4.200-20251216 · Dec 2025 · command-line history -
--output2.4.200-20251216 · Dec 2025 · command-line history
Artifact inspection verified suggested Outputs artifact data as JSON so it can be inspected directly or consumed by other tools.
Suggested capability: EVE JSON event output. This is our guess, not confirmed.
Also counts toward: CSV data export, JSON data export
release
- Adds CSV delimiter configuration and query name support for data export workflows. 2.4.190-20251024 · Oct 2025 · source · release history
- Adds support for nested keys in observable data structures 2.4.40-20240116 · Jan 2024 · source · release history
command line
-
artifact — the artifact represented in JSON format2.3.280-20231128 · Nov 2023 · command-line history
Exclusion controls in Detections shipped suggested Allows users to selectively exclude specific items from detection evaluations within the Detections module.
Suggested capability: Intrusion detection and rules. This is our guess, not confirmed.
release
- Adds an exclusion toggle in the UI for managing detection exclusions. 2.4.190-20251024 · Oct 2025 · source · release history
- Adds ignored SIDs management in the UI. 2.4.120-20250212 · Feb 2025 · source · release history
- Add Exclusion toggle provides a UI control to exclude specific items from detections within the Detections module 2.4.60-20240320 · Mar 2024 · source · release history
Process ancestry visualization shipped Displays full parent-child process relationships and trees within SOC case views.
release
- Adds Ruleset Name UI element for improved rule management display. 2.4.180-20250916 · Sep 2025 · source · release history
- New Process Ancestry action on the SOC Actions menu to show process tree 2.4.50-20240220 · Feb 2024 · source · release history
example
-
View the full parent-child relationship of a process from a SOC case view.
In the SOC Actions menu, select 'Process Ancestry' on an event to visualize the process tree.2.4.50-20240220 · Feb 2024 · source
Detections bulk indexing shipped Manages high-volume detection data ingestion with near-real-time refresh capabilities and configurable bulk indexer parameters.
release
- Adds a new limit on bulk creating related events to improve scalability. 2.4.120-20250212 · Feb 2025 · source · release history
- Reduces detection refresh interval to 1 second for near-real-time detection index updates. 2.4.90-20240729 · Jul 2024 · source · release history
- Introduces new configuration values for the Detections Bulk Indexer. 2.4.90-20240729 · Jul 2024 · source · release history
AI assistant model selection shipped Allows operators to choose from multiple AI models for the SOAI assistant, including Claude Haiku and Sonnet, with configurable context limits.
release
- Add Claude Haiku as an available SOAI assistant model alongside existing options. 3.4.0-20261102 · Nov 2026 · source · release history
- Raise the SOAI Sonnet default small context limit to 1 million tokens. 3.4.0-20261102 · Nov 2026 · source · release history
Detection annotation capability shipped Allows users to add annotations to existing detections for enhanced context and collaboration.
release
- Metric alarms and additional notification annotations expand alerting observability. 3.4.0-20261102 · Nov 2026 · source · release history
- Enables adding annotations to existing detections. 2.4.120-20250212 · Feb 2025 · source · release history
User role assignment on creation shipped Applies specified roles when adding new users rather than defaulting to a base role.
Also counts toward: Role-based access control
release
- Enables read-only SOC and Kratos modes. 3.1.0-20260521 · May 2026 · source · release history
- Applies specified role when adding new users instead of defaulting. 2.4.140-20250324 · Mar 2025 · source · release history
Bring Your Own Hypervisor deployment shipped Enables users to deploy the tool on custom hypervisors by mounting virtual disks for network security data storage.
release
-
Introduces hypervisor environment support with virtual disk management and a new
nsm_totalgrain. 2.4.200-20251216 · Dec 2025 · source · release history -
Adds Bring Your Own Hypervisor (BYOH) support, enabling users to create VMs that mount a virtual disk for
/nsm. 2.4.190-20251024 · Oct 2025 · source · release history
Hardware virtualization support shipped Enables hardware virtualization capabilities including libvirt states and salt.cloud execution on various nodes.
release
- Adds hardware virtualization support for manager/search and standalone nodes, including hypervisor firewall rules. 2.4.180-20250916 · Sep 2025 · source · release history
- Adds hardware virtualization support, including libvirt states and salt.cloud state execution on standalone and managersearch nodes. 2.4.170-20250812 · Aug 2025 · source · release history
HSTS enforcement for browser redirects shipped Enables HTTP Strict Transport Security (HSTS/STS) for browser redirects to enhance security.
release
- Enables HTTP Strict Transport Security (HSTS/STS) for browser redirects. 2.4.170-20250812 · Aug 2025 · source · release history
- Enables HTTP Strict Transport Security (STS) for browser redirects. 2.4.160-20250625 · Jun 2025 · source · release history
YARA rule compilation verified suggested Compiles YARA rules from a directory so they are ready to use in detection workflows.
Suggested capability: Intrusion detection and rules. This is our guess, not confirmed.
docs
- Free open Linux distribution for threat hunting, enterprise security monitoring, and log management with Elastic Stack, Suricata, and Zeek.
command line
-
rules_dir — Directory containing YARA rules to compile2.4.70-20240529 · May 2024 · command-line history
Custom container bind mounts shipped Supports user-defined volume mappings via custom bind mounts on tool containers such as so-kafka and so-soc.
release
-
Add
custom_bind_mountssupport toso-kafkaandso-soccontainers for custom volume mappings. 3.4.0-20261102 · Nov 2026 · source · release history
SOC UI display controls shipped Provides configurable settings for the SOC interface, including control over rendering of external images in markdown content.
release
-
Add
allowExternalMarkdownImagesSOC setting to control rendering of external images in markdown. 3.4.0-20261102 · Nov 2026 · source · release history
Unified automation workflows shipped Consolidates alert and notification automation into a single unified system for streamlined workflow management.
release
- Automations are now unified, consolidating alert and notification automation workflows into a single system. 3.4.0-20261102 · Nov 2026 · source · release history
Cloud marketplace deployment documented Provides an official Security Onion virtual machine image on the Azure Marketplace for deploying the tool in Azure environments.
docs
-
Azure Cloud Image Azure users can deploy an official Security Onion virtual machine image found on the Azure Marketplace:
https://securityonion.net/azureWarning Existing 2.4 RC1 or newer Security Onion Azure Image installations should use the soup command to upgrade to newer versions of Security Onion. docs update · Oct 2026 · source
Kernel and platform support shipped Supports the UEK8 kernel across installation and grid deployments for consistent platform behaviour.
release
- Adds UEK8 kernel support across install and grid, with UEK8 set as the boot default. 3.2.0-20260729 · Jul 2026 · source · release history
Elasticsearch retention estimation shipped Provides capability to estimate Elasticsearch data retention periods based on current indexing rates and storage capacity.
release
-
Adds Elasticsearch retention estimation capability (
so-elasticsearch-retention-estimate). 2.4.200-20251216 · Dec 2025 · source · release history
PCAP annotation capabilities shipped Allows analysts to add annotations and context to packet capture data directly within the investigation interface.
release
- Adds PCAP annotations, enabling analysts to annotate packet capture data within the interface. 2.4.200-20251216 · Dec 2025 · source · release history
Background config UI actions shipped Supports running long-running operations in the background via the configuration UI without blocking the interface.
release
- Supports background actions via the config UI, allowing long-running operations without blocking the interface. 2.4.150-20250512 · May 2025 · source · release history
Grid and subgrid SOC UI display shipped Adds additional grid and subgrid support in the SOC UI for richer data display.
release
- Adds additional grid and subgrid support in the SOC UI for richer data display. 2.4.150-20250512 · May 2025 · source · release history
Kafka external access shipped Enables external access to Kafka topics with username/password authentication for remote clients.
release
- Enables external access to Kafka topics via username/password authentication for remote clients. 2.4.150-20250512 · May 2025 · source · release history
Strelka scanner management shipped Ensures missing Strelka scanners are included and automatically restarts containers on configuration changes.
release
- Adds missing Strelka scanners and restarts Strelka containers automatically on config change. 2.4.150-20250512 · May 2025 · source · release history
Observer name in LDAP search shipped Includes `observer.name` in LDAP search results to provide richer event context.
release
- Includes observer.name in ldap_search results for richer event context. 2.4.140-20250324 · Mar 2025 · source · release history
Managed integration license support shipped Enables the installation of Elastic integrations that require a specific Elastic license.
release
- Enables installation of Elastic integrations that require an Elastic license. 2.4.130-20250311 · Mar 2025 · source · release history
Multiline input configuration support shipped Adds multiline input support for managed integration configuration fields in the UI.
release
- Adds multiline input support for managed integration configuration fields. 2.4.130-20250311 · Mar 2025 · source · release history
TLSv1.3 support in nginx shipped suggested Enables TLSv1.3 support in the nginx configuration for improved security protocols.
Suggested capability: New protocol support (added dissectors). This is our guess, not confirmed.
release
- Adds TLSv1.3 support to the nginx configuration. 2.4.130-20250311 · Mar 2025 · source · release history
Cloudflare Logpush integration shipped suggested Adds support for Cloudflare Logpush integration to ingest firewall logs.
Suggested capability: Network traffic logging. This is our guess, not confirmed.
release
- Adds Cloudflare Logpush integration support. 2.4.120-20250212 · Feb 2025 · source · release history
Detection tuning notes shipped suggested Supports adding tuning notes to detections to track calibration efforts and results.
Suggested capability: Intrusion detection and rules. This is our guess, not confirmed.
release
- Adds tuning notes capability to detections. 2.4.120-20250212 · Feb 2025 · source · release history
External threat intelligence integration shipped Allows integration with external threat intelligence platforms to enrich detection and investigation contexts.
release
-
Adds OpenCTI threat intelligence (
ti_opencti) integration support. 2.4.120-20250212 · Feb 2025 · source · release history
Process ancestry event mappings shipped Adds specific mappings for process and file creation events to support enhanced lineage tracking.
release
- Adds process and file creation event mappings. 2.4.120-20250212 · Feb 2025 · source · release history
Trend Micro integration shipped Adds support for Trend Micro integration to extend endpoint and email security visibility.
release
- Adds Trend Micro integration support. 2.4.120-20250212 · Feb 2025 · source · release history
External detections management API shipped suggested Provides external integration points for managing detection rules and configurations.
Suggested capability: Rule source management and updates. This is our guess, not confirmed.
release
- Adds external support for Detections management. 2.4.110-20241004 · Oct 2024 · source · release history
Artifact repository integration shipped Provides integration with the Elastic Artifact Repository to allow users to access and manage external artifacts directly within the platform.
release
- Adds Integrate Elastic Artifact Repo for accessing external artifacts within the platform. 2.4.2 · Jun 2023 · source · release history
EQL to playbook integration shipped suggested Enables the execution of Event Query Language (EQL) queries within automated detection and response playbooks.
Suggested capability: Intrusion detection and rules. This is our guess, not confirmed.
release
- Adds EQL to Playbook support enabling Event Query Language queries within automated response workflows. 2.4.2 · Jun 2023 · source · release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
No command matches.
| option | found in | since | description |
|---|
Values are placeholders taken from each option’s declared default. Nothing is executed here — the output shown is a recording of a run that already happened.
Screenshots
From the release notes, newest first. Click one to see it full size.Media
Videos from the release notes, newest first. They play right here.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
- Community health
-
Contributor trend distinct committers, this year against last
-
Maintainer concentration bus factor now against a year ago
-
Issue backlog trend issues closed per issue opened, 12 months
-
Responsiveness median time to a maintainer’s first reply
Nine scores for Security Onion, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Security Onion puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Coverage
Missing something? Tell us
What Security Onion connects to, runs on and detects, read from its release notes and docs. So far: 4 updated supported platforms.
4 changes, tracked since Nov 2, 2026.
-
Nov 22026
updated Suricata updated to 8.0.8
Suricata to 8.0.8
-
Nov 22026
updated Zeek updated to 8.0.11
Zeek to 8.0.11
-
Nov 22026
updated Elasticsearch updated to 9.4.8
Elasticsearch to 9.4.8
-
Nov 22026
updated ElastAlert2 updated to 2.32.0
ElastAlert2 to 2.32.0
Databases & data platforms 1
Other 3
Nothing first seen in this window. That doesn't mean Security Onion shipped nothing, only that we found no record of it.
How we count
Read from 2 of 36 release notes and docs updates we hold for Security Onion. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through Security Onion's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
36 entries
No entries match these filters.
- November 20262
- October 20261
- September 20263
- July 20261
- May 20261
- March 20263
- December 20251
- October 20251
- September 20251
- August 20251
- June 20251
- May 20251
- March 20252
- February 20251
- October 20241
- August 20241
- July 20241
- June 20241
- May 20241
- March 20241
- February 20241
- January 20241
- November 20231
- October 20231
- August 20232
- July 20232
- June 20231
- November 20201
Project health
Issue, contributor and maintainer activity in Security-Onion-Solutions/securityonion, 2023-10 – 2026-09, as of 2026-09-25. Twelve-month figures first; the trend lines run the whole window.
- Contributors 12 +1 vs prior 12 months
- Maintainers 4 +1 joined · −1 left, last 12 months
- Bus factor 2 committers behind half the commits
- Community-filed 100% of issues opened, last 12 months
- Median time to close 6.8 days first maintainer reply 2.9 days
- Open backlog 76 of 2,979 issues ever filed
- Issues opened / month 11 · 0 communitymaintainers
- Open backlog 76
- Contributors / month 5
- Commits / month 17
- Stars 4,889
- other 100%
Counts from the project's public repository and git history; no individuals are identified. Maintainers are the committers covering 80% of the last year's commits. how we measure this
Articles
1 article · updated Nov 4, 2026Where Security Onion turns up in what others publish: how-tos, attack reports that name it, and incident write-ups. A row says why it is here and quotes where the article names it; the link goes to the publisher.
Tutorials & guides 1
-
Security Onion Configuration in VMware
Security Onion is a Linux distro for intrusion detection, network security monitoring, and log management.
2 more quotes
Security Onion effortlessly merges collectively two main roles i.e.
HIDS: Security Onion offers OSSEC for host-based intrusion detection.
Libraries its release ships
What its latest release locks, checked against known advisories.None of its release's images build from a lockfile we can read.
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →