Wallarm
Introducing a New API Discovery Dashboard (2026-10-13) commercialThe section your link pointed to isn't on Wallarm's page any more, so we've brought you to the top.
Summary
Wallarm is a commercial web-app-security platform that discovers, protects, and tests APIs and AI-driven workloads against attacks like the OWASPOWASPA nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. API Top 10, abuse, and account takeover. It runs as a managed (Security Edge) or self-hosted node, deployable into Kubernetes, cloud platforms, API gateways, or CDNs, and is aimed at SOCSOCA security operations center, the team or function that monitors threats, investigates alerts and coordinates incident response. Its work can be internal, outsourced or shared. analysts and API security teams who need to investigate incidents rather than just detect them — the console lets analysts drill into request-level attack data, group related requests, and build scoped dashboards for ongoing monitoring. Its Infrastructure Discovery module extends this to AWS estates, mapping attack pathsattack pathsA possible sequence of steps an attacker could take to reach a valuable target. It connects weaknesses, permissions and reachable systems rather than treating each finding separately. through IAMIAMIdentity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access. and configuration relationships to show which single fix would break the most attacker routes, independent of CVE findings. Launched in 2013, it remains actively developed, with 21 releases in the tracked window and its most recent just 22 days old.
How Wallarm helps
Which requests behind an attack are actually part of the same incident?
clusters attacking requests by attack type, source IP, host, path, or a custom combination, surfacing patterns a single request view would miss
Can an attacker chain role assumptions and policy attachments into effective admin somewhere in our account?
follows IAM chains — role chaining, pass-role, self-escalation, policy attachment — and shows where they lead to effective-admin
Are our AWS security findings actually exploitable, or just sitting in a list?
overlays Security Hub, Inspector, and GuardDuty findings onto the attack path map to raise priority, but still surfaces paths even when no finding exists along the chain
Which of our assets are the ones actually worth protecting first?
lets a team pin its own crown jewels from the console so path severity scoring reflects real business priorities instead of default assumptions
What exactly did a given attack request contain, down to the payload and headers?
drills from a single attack into full request-level detail — source IP, host, URI, payload, parameters, classifications, headers, and the raw request
Languages
Features
Built from Wallarm's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- Wallarm covers 1 of the 2 vulnerability management capabilities we track.
What Wallarm offers you
- Web management console11
- Kubernetes-native deployment3
- GraphQL API support2
- Outbound webhooks (the product notifies you)2
- User-defined detection rules2
- Agent-based deployment1
- Command-line interface1
- CSV data export1
- gRPC API support1
- JSON data export1
- ML-based detection1
- Scheduled jobs1
- Scripting language support1
- SIEM forwarding1
- REST API
No capabilities match.
All capabilities 80 capabilities
Console navigation and UI structure shipped Introduces a side-positioned main menu for system-wide navigation and restructures the scanner section with vulnerability visibility.
Also counts toward: Web management console
release 26 total
-
Adds a step-by-step rule builder that constrains each step to valid options (e.g. Cookie → JWT → Base64 → JSON → sub).
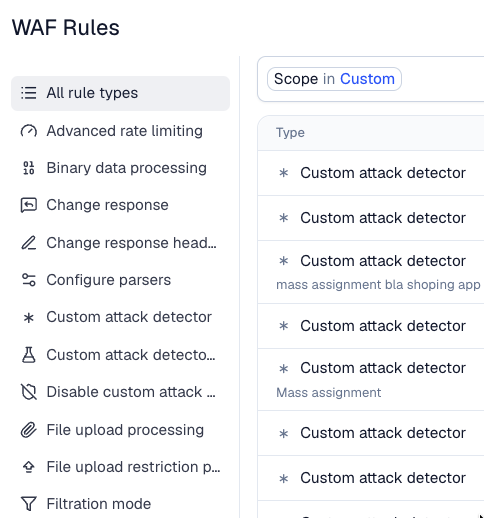 Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026
· source
· release history
-
Shows the full request-targeting path inline on each rule row (e.g.
HEADER › AUTHORIZATION › JWT › jwt_header › BASE64 › JSON › alg) without opening individual rules. Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source · release history - Adds application and scope filters — distinguishing Default (Wallarm-managed, read-only) rules from team-created rules — persisted in the address bar across reloads. Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source · release history
- Displays the full nested request targeting path (e.g., HEADER › AUTHORIZATION) on each rule row for immediate visibility Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source · release history
- Enables inline enable/disable, duplicate, and delete actions directly from the rules list Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source · release history
- Adds address bar filters to persist views by application or Default status across reloads Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source · release history
docs
- Go to Wallarm Console â â To add session grouping keys manually, go to Wallarm Console â â RESPONSE â BODY JSON â PROPERTY â token REQUEST â QUERY â token REQUEST â BODY â JSON â PROPERTY â token RESPONSE â BODY â JSON â PROPERTY â token REQUEST â QUERY â token REQUEST â BODY… seen Aug 2026 · source
example 7 total
-
Audit rule coverage for deeply nested payload structures without opening individual rules.
In the Rules panel, examine the targeting path column to see entries like 'HEADER › AUTHORIZATION › JWT › jwt_header › BASE64 › JSON › alg' and identify which rules affect specific nested fields.Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source -
Manage rule states efficiently by filtering only non-editable system rules.
Use the scope filter in the address bar to separate 'Default' (non-editable) rules from team-created ones, then use the inline actions to disable or duplicate rules as needed.Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source -
Find which rules cover a specific deeply nested JWT parameter without opening each rule individually.
In the Wallarm dashboard, go to WAF Rules, select the rule type filter for the relevant rule type, then read the targeting path on each row — e.g.announced · Sep 2026 · source -
Save a view for a specific application's attack patterns with custom columns and time range.
In the Attacks interface, configure columns and filters, then click 'Save View' to create a dedicated dashboard.Introducing the New Attacks Interface (2026-07-02) · Jul 2026 · source -
Navigate traffic trends and apply filters directly from the new interactive Dashboard charts.
In the Wallarm dashboard, click 'Attacks' to open the new interface and use chart filters to narrow the scope.Introducing the New Attacks Interface (2026-07-02) · Jul 2026 · source -
Group requests by source IP to identify coordinated attack patterns.
In the Attacks interface, select 'Interactive Request Grouping' and choose 'source IP' as the grouping key.Introducing the New Attacks Interface (2026-07-02) · Jul 2026 · source
API Discovery and Classification shipped Automatically discovers, classifies (internal/external), and tracks changes in APIs across the estate to maintain an accurate inventory.
release 18 total
- Adds the Dashboards → Discovered inventory dashboard surfacing internet-exposed APIs, unauthenticated endpoints, shadow and zombie APIs, and open security issues in a single view.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Introducing a New API Discovery Dashboard (2026-10-13) · Oct 2026 · source · release history
- Adds an unauthenticated endpoints filter to the inventory view to quickly list exposed APIs Know exactly how every API endpoint is authenticated (2026-05-05) · May 2026 · source · release history
- Adds consistent, partial, and missing authentication classifications for every API endpoint based on rolling 7-day production traffic analysis Know exactly how every API endpoint is authenticated (2026-05-05) · May 2026 · source · release history
- Adds Detection of WAAP solutions for each open port to identify coverage gaps on non-standard ports Improvements to API Attack Surface Management · Sep 2024 · source · release history
- Expands API Gateway Detection support to 15 specific vendors (including Apigee, Mulesoft, Kong, WSO2) Improvements to API Attack Surface Management · Sep 2024 · source · release history
- Enhanced OpenAPI data type detection by the API Discovery module Wallarm Node 4.10.6 · May 2024 · source · release history
docs
- â full operational surface: API discovery, attack monitoring, rules, integrations, mitigation controls, sessions, and more. (AWS-only) â cross-account AWS asset discovery and the relationship graph (when active on the subscription). â vulnerability findings from passive detection and AASM. seen Aug 2026 · source
-
API Discovery analyzes legitimate traffic locally â it inspects which endpoints are requested and what parameters are passed in requests and responses.
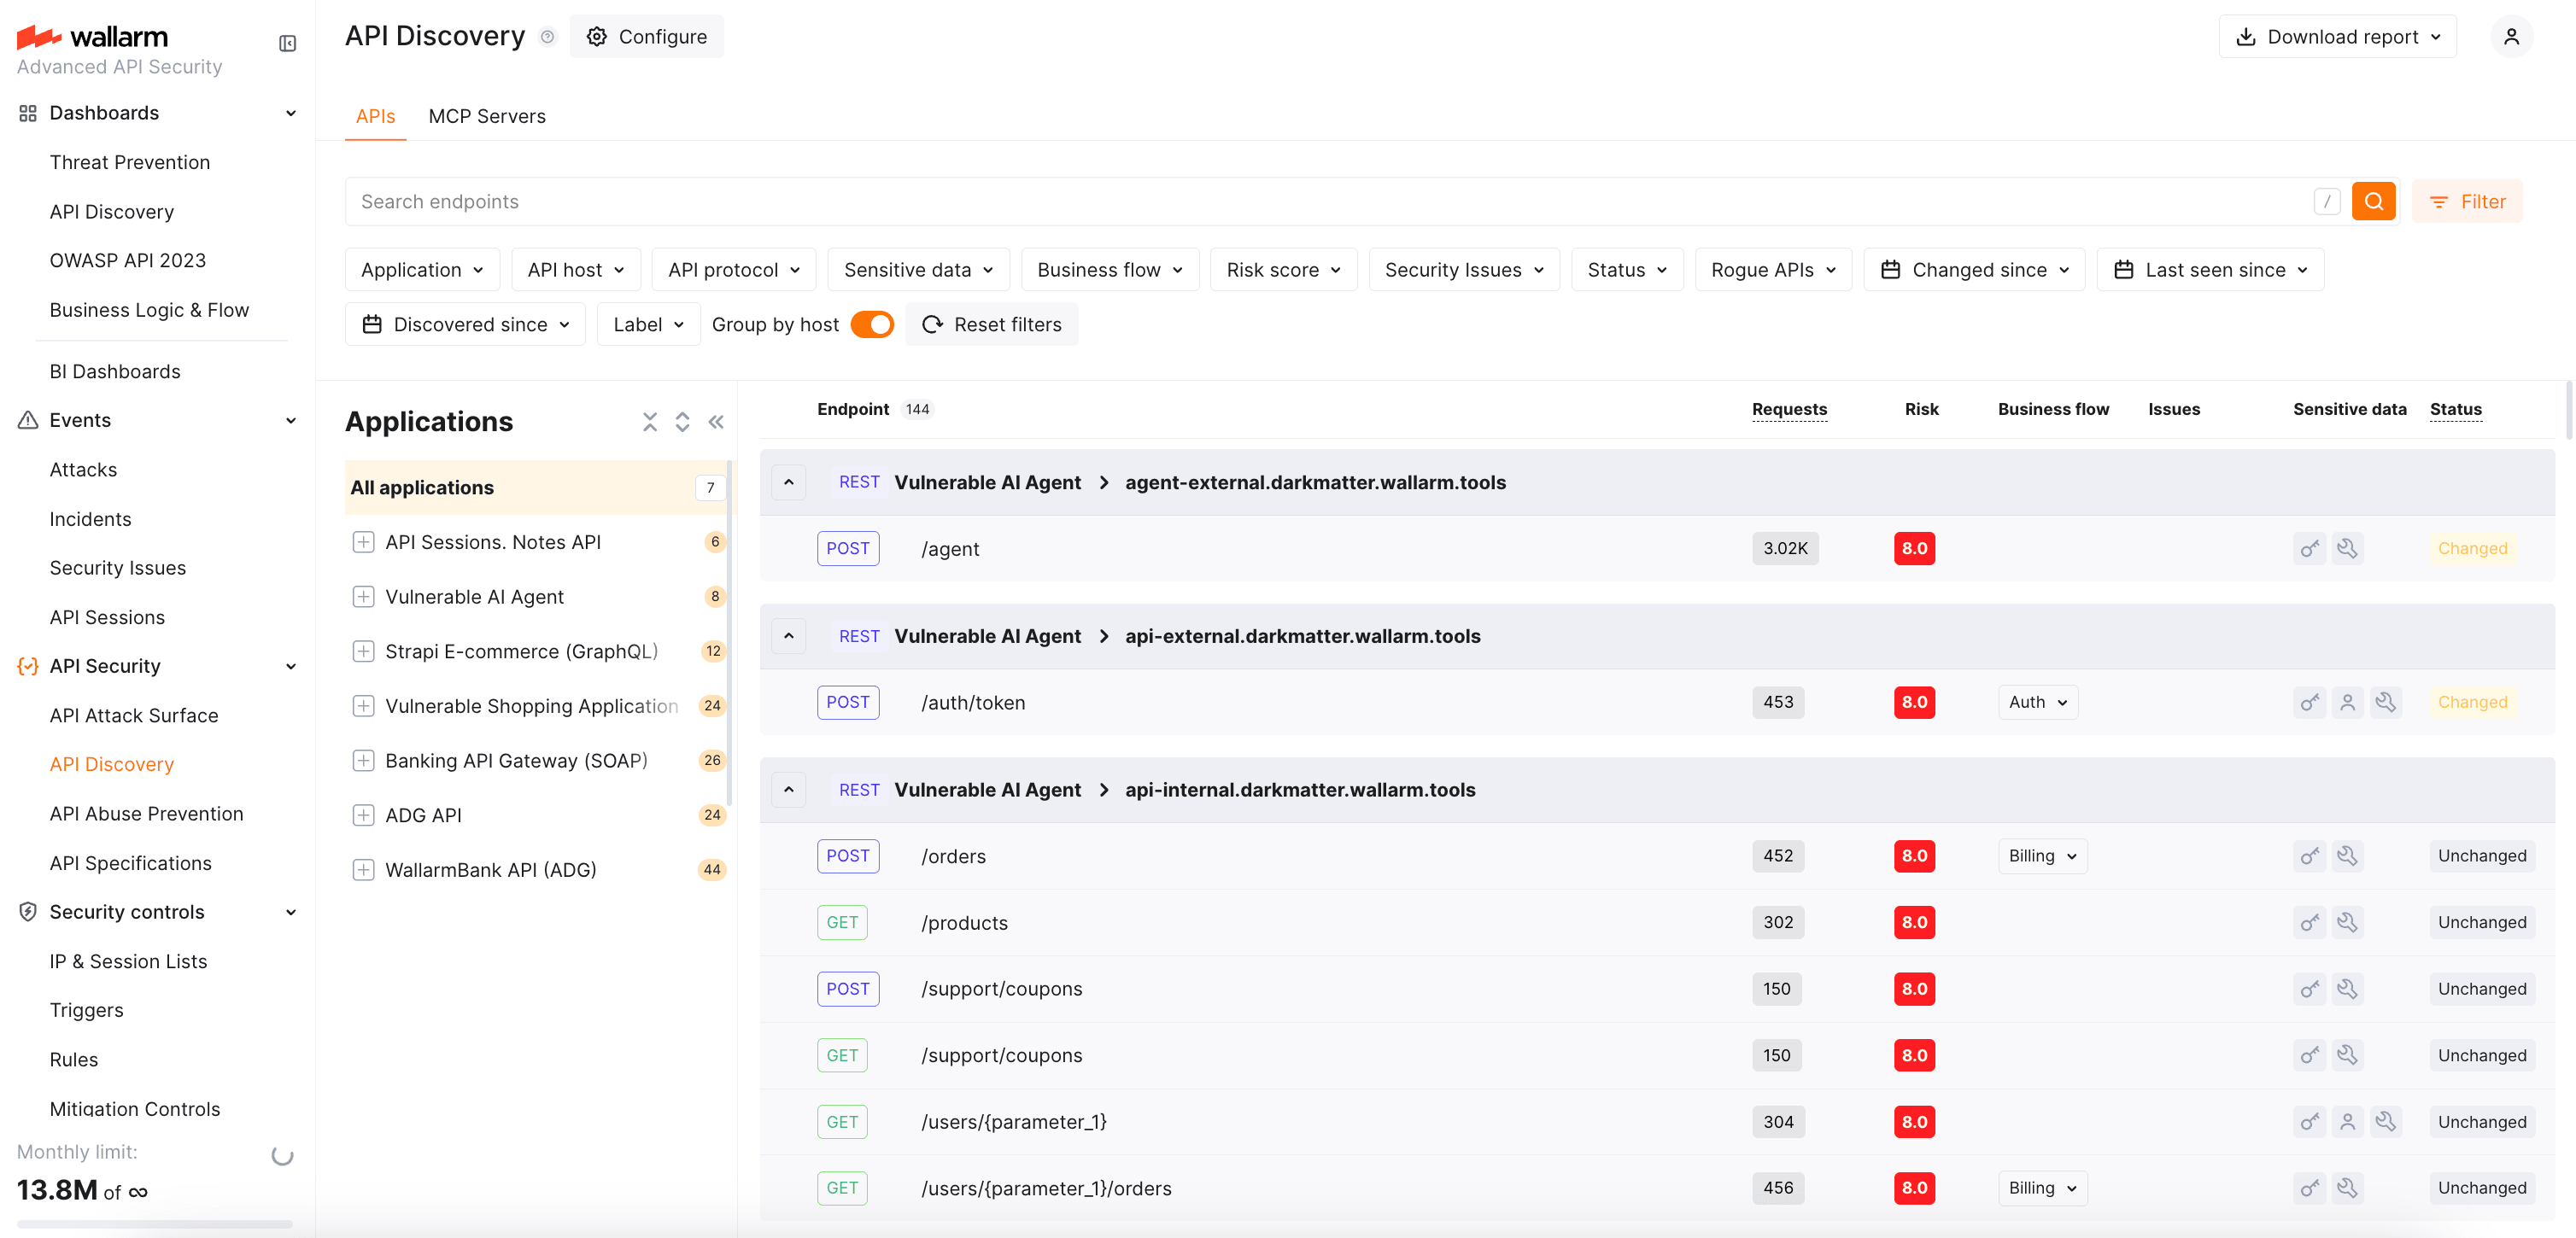 docs update · Aug 2026
· source
- â Find undocumented endpoints (in traffic but not in any of your specs). â Find deprecated endpoints that still handle traffic (removed from spec but still in use). seen Aug 2026 · source
- and discovery starts over from scratch â past parameter information and history are not recovered. â daily or hourly summaries of new and changed endpoints, delivered to your account email and any additional addresses. seen Aug 2026 · source
example
-
Review your full API attack surface — including shadow and zombie APIs — without any setup or migration.
In the Wallarm console, go to Dashboards → Discovered inventory to view internet-exposed APIs, unauthenticated endpoints, shadow and zombie APIs, and open security issues at a glance.Introducing a New API Discovery Dashboard (2026-10-13) · Oct 2026 · source -
Find APIs lacking consistent authentication in your inventory.
Open API Discovery inventory, apply filter 'Authentication status: Missing'.Know exactly how every API endpoint is authenticated (2026-05-05) · May 2026 · source
Attacks dashboard shipped An interactive dashboard for exploring attack trends, filtering by application, attack type, host, and other dimensions, and saving scoped views for ongoing investigation.
release 18 total
-
Adds a time-series chart of requests with incidents alongside breakdowns of top source IPs, endpoints, hosts, attack types/subtypes, and application response codes over a rolling month.
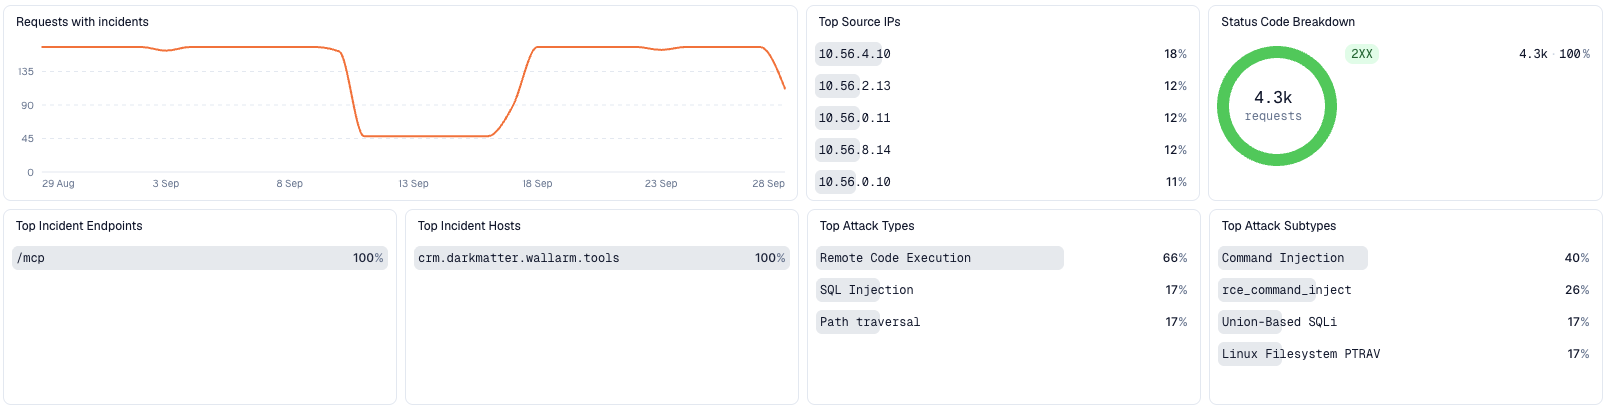 announced · Sep 2026
· source
· release history
- Encodes active filters and time range in the page URL so dashboards can be bookmarked, reloaded, or shared in tickets and the same view opens for recipients. announced · Sep 2026 · source · release history
- Provides a time-series chart of requests with incidents alongside top source IPs, endpoints, hosts, attack types and subtypes, and a breakdown of application response codes over the past month. Introducing the New Incidents Interface (2026-09-29) · Sep 2026 · source · release history
- Encodes active filters and time range in the page URL, enabling bookmarking and sharing a specific incident view via link. Introducing the New Incidents Interface (2026-09-29) · Sep 2026 · source · release history
- New interactive Attacks dashboard lets analysts navigate attack trends, spot anomalies, and apply filters directly from charts, tables, and statistics. Introducing the New Attacks Interface (2026-07-02) · Jul 2026 · source · release history
- Customizable Views enable saving preferred columns, filters, time ranges, and groupings as dedicated dashboards scoped to specific attack types, applications, hosts, or incidents. Introducing the New Attacks Interface (2026-07-02) · Jul 2026 · source · release history
example
-
Share the exact filtered incident view with a teammate or embed it in a ticket so they land on the same scope without manual filter reconstruction.
In the Incidents page, apply your filters (attack type, time range, endpoint, etc.), then copy the page URL from the browser address bar and paste it into your ticket or chat.announced · Sep 2026 · source -
Scope an investigation to a specific application and attack type, then export the filtered results for an incident report.
In the Wallarm console, go to Attacks > apply filters for the target application and attack type > set your time range > select columns relevant to the incident > click Export to download the…Introducing the New Attacks Interface (2026-07-02) · Jul 2026 · source -
Create a persistent dashboard for a specific host so the SOC team always has a scoped view ready without re-applying filters each session.
In the Wallarm console, go to Attacks > set filters for the target host and preferred columns and time range > click Save View > name the view and assign it as a dedicated dashboard for that host.Introducing the New Attacks Interface (2026-07-02) · Jul 2026 · source
Unified WAF traffic view shipped Provides a consolidated view of malicious payload traffic and application breakdowns across multiple apps or APIs.
Also counts toward: Web management console
release 17 total
- Scan single IPs, subnets, and CIDR ranges in addition to domains via the AASM Configuration screen AASM Updates — broader visibility, faster validation, clearer reporting (2026-03-26) · Mar 2026 · source · release history
- Enables simplified deployment by removing the need for traffic mirroring or custom forwarding logic Wallarm Now Natively Supports IBM DataPower API Gateway · May 2025 · source · release history
- Enables download of a WAAP Score Evaluation report containing attack detection types and false-positive rates Improvements to API Attack Surface Management · Sep 2024 · source · release history
- Added support for NGINX v1.26.0 Wallarm Node 4.10.6 · May 2024 · source · release history
- Adds support for NGINX v1.25.4 in Wallarm Nodes Wallarm Nodes 4.10.2 - 4.10.4 releases and 4.8.9 performance update · Apr 2024 · source · release history
-
Upgrades the embedded NGINX version in the Wallarm node Docker image to
1.24.0Introducing Wallarm Node 4.10 · Feb 2024 · source · release history
example
-
Discover hidden internet-facing assets by scanning a specific network block rather than just known domains.
Navigate to AASM Configuration and add your target CIDR range (e.g., `192.168.1.0/24`) to the scan targets list.AASM Updates — broader visibility, faster validation, clearer reporting (2026-03-26) · Mar 2026 · source
Infrastructure attack path analysis shipped Visualizes end-to-end attacker routes through AWS estates — including IAM chains, choke points, and crown jewels — built from configuration and IAM relationships rather than CVE findings.
release 12 total
- New Attack Paths feature in Infrastructure Discovery visualizes end-to-end attacker routes through AWS estates, built from configuration and IAM relationships rather than CVE findings. See how an attacker would reach your critical AWS assets (2026-07-30) · Jul 2026 · source · release history
- Attack Paths is included in the existing Infrastructure Discovery license with no additional SKU or add-on charge. See how an attacker would reach your critical AWS assets (2026-07-30) · Jul 2026 · source · release history
- Crown jewels are user-defined: pin and unpin assets from the console to reprioritize path scoring around your own high-value targets. See how an attacker would reach your critical AWS assets (2026-07-30) · Jul 2026 · source · release history
- Paths are ranked by severity and displayed as a map showing entry points, pivot nodes, choke points, and crown jewels with plain-English explanations. See how an attacker would reach your critical AWS assets (2026-07-30) · Jul 2026 · source · release history
- Choke point identification surfaces nodes through which the most attack paths run, highlighting where a single remediation has the greatest blast-radius reduction. See how an attacker would reach your critical AWS assets (2026-07-30) · Jul 2026 · source · release history
- Identity-aware path analysis follows IAM chains including role chaining, pass-role, policy attachment, self-escalation, and effective-admin through AWS managed policies. See how an attacker would reach your critical AWS assets (2026-07-30) · Jul 2026 · source · release history
docs
- Attack path analysis — chains individual misconfigurations into complete routes from an exposed resource to a valuable one, and identifies the single resource that breaks the most routes at once. docs update · Jul 2026 · source
example
-
Define your own crown jewels so path severity scoring reflects your business priorities rather than default assumptions.
In the Wallarm console, go to Infrastructure Discovery → Attack Paths, select an asset on the map, and use Pin / Unpin to mark it as a crown jewel. Path scores recalculate immediately.See how an attacker would reach your critical AWS assets (2026-07-30) · Jul 2026 · source -
Navigate to the new Attack Paths view to see ranked attacker routes through your connected AWS accounts.
In the Wallarm console, go to Infrastructure Discovery → Attack Paths to view the ranked path map for your connected AWS accounts.See how an attacker would reach your critical AWS assets (2026-07-30) · Jul 2026 · source
Security event integration shipped Enables sending security events and system messages to external platforms such as Splunk, Rapid7 InsightConnect, and Webhooks.
Also counts toward: Outbound webhooks (the product notifies you)
release 15 total
- Enables exporting dashboard charts to PDF for leadership briefings Meet Your New Favorite API Security Dashboards (2026-01-22) · Jan 2026 · source · release history
- Enables turning on/off the auto-rescan scheduler per domain in AASM More Control and Accuracy in Scan Scope Configuration in API Attack Surface Management · May 2025 · source · release history
- Includes a new internal GraphQL parser in Wallarm node version 5.3.0+ Full-Fledged GraphQL Parser · Feb 2025 · source · release history
- Adds Jira integration to automatically create issues for detected vulnerabilities Simplify Vulnerability Management with Wallarm's Jira integration · May 2023 · source · release history
- Wallarm introduces a native integration with Microsoft Azure Sentinel to streamline API security operations. Streamline Your API Security Operations with Wallarm's Azure Sentinel Integration · Mar 2023 · source · release history
- Enables notifications for API changes via Slack, SIEMs, and SOARs through the API Discovery module Introducing the Wallarm API Discovery Dashboard · Mar 2023 · source · release history
Rule Builder and Management UI shipped Provides an interactive, panel-based interface for creating, editing, filtering, and auditing WAF rules with support for nested path visualization and scoped sharing.
Also counts toward: User-defined detection rules, Web management console
release 9 total
-
Adds a step-by-step rule builder that constrains each step to valid options (e.g. Cookie → JWT → Base64 → JSON → sub).
Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026
· source
· release history
-
Shows the full request-targeting path inline on each rule row (e.g.
HEADER › AUTHORIZATION › JWT › jwt_header › BASE64 › JSON › alg) without opening individual rules. Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source · release history - Adds application and scope filters — distinguishing Default (Wallarm-managed, read-only) rules from team-created rules — persisted in the address bar across reloads. Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source · release history
- Displays the full nested request targeting path (e.g., HEADER › AUTHORIZATION) on each rule row for immediate visibility Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source · release history
- Enables inline enable/disable, duplicate, and delete actions directly from the rules list Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source · release history
- Adds address bar filters to persist views by application or Default status across reloads Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source · release history
example
-
Audit rule coverage for deeply nested payload structures without opening individual rules.
In the Rules panel, examine the targeting path column to see entries like 'HEADER › AUTHORIZATION › JWT › jwt_header › BASE64 › JSON › alg' and identify which rules affect specific nested fields.Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source -
Share a filtered rules view scoped to a specific application with a teammate so they can review coverage without navigating the tree.
In the Wallarm dashboard, go to WAF Rules, apply the application filter for your target app and set the scope filter to show only team-created rules (excluding 'Default'), then copy the URL from the…Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source -
Manage rule states efficiently by filtering only non-editable system rules.
Use the scope filter in the address bar to separate 'Default' (non-editable) rules from team-created ones, then use the inline actions to disable or duplicate rules as needed.Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source -
Find which rules cover a specific deeply nested JWT parameter without opening each rule individually.
In the Wallarm dashboard, go to WAF Rules, select the rule type filter for the relevant rule type, then read the targeting path on each row — e.g.announced · Sep 2026 · source -
Bookmark a filtered view of all WAF rules applied to the production app.
Navigate to the new Rules panel in the Wallarm dashboard, select the 'Production' application filter from the address bar, and bookmark the resulting URL.Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source
Incidents page shipped A dedicated dashboard page showing only confirmed incidents — attacks that hit a real vulnerability and received a confirming response — with inline Security Issues status, links from Threat Prevention and Security Issues, shareable filtered views, and export for reporting or incident response.
release 10 total
-
Shows severity and open/closed state of linked Security Issues in a Security Issues column on every incident row without requiring a click-through.
announced · Sep 2026
· source
· release history
- Adds shareable incident views via URL-encoded filters and time ranges. Introducing the New Incidents Interface (2026-09-29) · Sep 2026 · source · release history
- Adds an export capability for the incidents in the current filtered view, for use in incident response or reporting. Introducing the New Incidents Interface (2026-09-29) · Sep 2026 · source · release history
- Adds a Security Issues column on every incident row showing the severity and open/closed state of each linked issue without requiring a click-through. Introducing the New Incidents Interface (2026-09-29) · Sep 2026 · source · release history
- Adds a new Incidents page in the dashboard showing only confirmed incidents — attacks that hit a real vulnerability and received a response proving it worked.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Introducing the New Incidents Interface (2026-09-29) · Sep 2026 · source · release history
- Adds the Incidents page to the Wallarm dashboard for viewing confirmed attacks that resulted in a response. Introducing the New Incidents Interface (2026-09-29) · Sep 2026 · source · release history
docs
- Open Wallarm Console â , open Wallarm Console â â â To find BOLA attacks, set the Attack Type filter to Broken Object Level Authorization . Filtering is described in Attack Search and Filters seen Aug 2026 · source
example
-
Share the exact incident view — with filters and time range intact — directly into a ticket or Slack thread so teammates land on the same context.
In the Incidents page, apply your desired filters (e.g. attack type, host, time range), then copy the URL from your browser address bar and paste it into your incident ticket.Introducing the New Incidents Interface (2026-09-29) · Sep 2026 · source -
Share a specific view of confirmed incidents with colleagues or for ticketing without recreating the filter context.
Copy the URL from the browser address bar after applying filters and time ranges on the Incidents page.Introducing the New Incidents Interface (2026-09-29) · Sep 2026 · source
Detection extension configuration shipped Allows granular enabling, disabling, and filtering of detection extensions by technology or vulnerability type within the scanner settings.
Also counts toward: Web management console
release 13 total
-
Adds support for managing
wallarm_credential_stuffing_ruleresources in the Terraform provider Effortlessly manage security controls via Terraform provider · Sep 2024 · source · release history - Detects JWT weaknesses such as unsigned tokens and compromised signing keys Wallarm node 4.4 - checking JSON Web Token strength · Nov 2022 · source · release history
-
Adds
native integrationsupport for Kong Ingress Controller 3.0, enabling API protection for both Kong Open-Source (CE) and Enterprise (EE) editions Native integration with Kong Ingress Controller · Nov 2022 · source · release history - New configuration parameter allows specifying the NGINX service port inside the Docker image. Wallarm Node 3.6 released · Feb 2022 · source · release history
- Expands rules for detecting Local File Inclusion (LFI) attacks Updates from Wallarm’s detection team (April 2021) · Mar 2021 · source · release history
- Adds detection for new Remote Code Execution (RCE) attacks against Symphony Updates from Wallarm’s detection team (April 2021) · Mar 2021 · source · release history
Platform compatibility updates shipped Adds support for new operating systems and platform stacks (Debian 10, Amazon Linux 2, Heroku-18) to the filtering node.
release 12 total
- Adds Customizable Export to export filtered attack data for incident response, reporting, compliance, or offline analysis. Introducing the New Attacks Interface (2026-07-02) · Jul 2026 · source · release history
- Adds export of complete request and response logs for troubleshooting and reporting API Security Testing Keeps Getting Better (2026-02-16) · Feb 2026 · source · release history
- Applies rules across API Attack Surface Management, Threat Replay Testing, Passive Detection, and Schema-Based Testing Less Noise. More Signal. · Feb 2026 · source · release history
- Adds various Web-Shell upload detection rules for Wallarm Scanner. Updates from Wallarm’s detection team (August 2022) · Aug 2022 · source · release history
-
Added
alma-linuxandrocky-linuxplatform support for Wallarm Node deployments. Wallarm Node 3.6 released · Feb 2022 · source · release history - Added support for CloudLinux OS 6.x Wallarm Node 3.4 released · Nov 2021 · source · release history
Attack data export shipped Configurable export of attack data filtered by time range, columns, groupings, and other criteria for use in incident response, compliance, or offline analysis.
release
-
Adds export of the current filtered incident view for use in incident response or reporting workflows.
announced · Sep 2026
· source
· release history
- Customizable Export tailors attack data exports by filter, column selection, time range, and grouping for incident response, compliance, or offline analysis. Introducing the New Attacks Interface (2026-07-02) · Jul 2026 · source · release history
- Automated security report enables identification of critical risks and application of protective measures Protect Your APIs from OWASP API Security Top-10 2019 & 2023 · May 2023 · source · release history
example
-
Export a filtered incident list for post-incident reporting or feeding into an external SIEM after a critical RCE wave.
In the Incidents page, set your filters (e.g. attack type = RCE, time range = last 7 days), then click Export to download the incidents in your current view.Introducing the New Incidents Interface (2026-09-29) · Sep 2026 · source -
Share a filtered rule view with a teammate so they see only rules scoped to a specific application.
In WAF Rules, apply the application filter for your target app and copy the resulting URL from the address bar — the filter state is encoded in it and will reload correctly for anyone you share it…
announced · Sep 2026
· source
-
Share a filtered rules view scoped to a specific application with a teammate so they can review coverage without navigating the tree.
In the Wallarm dashboard, go to WAF Rules, apply the application filter for your target app and set the scope filter to show only team-created rules (excluding 'Default'), then copy the URL from the…Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source -
Bookmark a filtered view of all WAF rules applied to the production app.
Navigate to the new Rules panel in the Wallarm dashboard, select the 'Production' application filter from the address bar, and bookmark the resulting URL.Introducing the New WAF Rules Interface (2026-09-16) · Sep 2026 · source -
Scope an investigation to a specific application and attack type, then export the filtered results for an incident report.
In the Wallarm console, go to Attacks > apply filters for the target application and attack type > set your time range > select columns relevant to the incident > click Export to download the…Introducing the New Attacks Interface (2026-07-02) · Jul 2026 · source
Attack request investigation shipped Drill-down view that surfaces request-level details — source IP, host, URI, payload, parameters, classifications, headers, and raw request — from a single interface.
release
-
Groups incidents by attack type, HTTP method, domain, path, and the parameter the payload landed in, with drill-down to individual requests.
announced · Sep 2026
· source
· release history
- Groups incidents by attack type, HTTP method, domain, path, and payload parameter, with drill-down through each level to individual requests. Introducing the New Incidents Interface (2026-09-29) · Sep 2026 · source · release history
- Groups incidents by attack type, HTTP method, domain, path, and parameter, allowing drill-down to individual requests. Introducing the New Incidents Interface (2026-09-29) · Sep 2026 · source · release history
- Interactive Request Grouping lets analysts cluster attacking requests by attack type, source IP, host, path, or any custom combination to surface hard-to-spot patterns. Introducing the New Attacks Interface (2026-07-02) · Jul 2026 · source · release history
- Adds an Attack Investigation Flow to drill into individual attacks for request-level details including source IP, host, URI, payload, parameters, classifications, headers, and raw request data. Introducing the New Attacks Interface (2026-07-02) · Jul 2026 · source · release history
- Attack Investigation Flow surfaces request-level details — source IP, host, URI, payload, parameters, classifications, headers, and full raw request — from a single drill-down. Introducing the New Attacks Interface (2026-07-02) · Jul 2026 · source · release history
docs
- , the request details work the same way: open the incident, switch to the tab, select a request, and use the field menu. seen Sep 2026 · source
example
-
Investigate a confirmed attack by drilling into the specific request payload that triggered it within the new dashboard.
Navigate to 'Incidents' in the Wallarm dashboard, then drill down by grouping filters (attack type > HTTP method > path).Introducing the New Incidents Interface (2026-09-29) · Sep 2026 · source
Test record reuse and duplication shipped Enables creating similar test runs from existing test records to bypass the recording phase for repetitive security tests.
Also counts toward: Agent-based deployment
release
- Allows defining success criteria per test run in the UI to specify which severity levels mark a test as failed Schema-Based Testing Improvements · Nov 2025 · source · release history
- Adds the Generate test run command wizard to prepare Docker commands for test runs Schema-Based Testing Improvements · Nov 2025 · source · release history
- Adds status tracking and filtering options for test results Schema-Based Testing Improvements · Nov 2025 · source · release history
- Adds support for running tests via a lightweight Docker-based agent for isolated execution. Shift Left: Find API Vulnerabilities Faster · Sep 2025 · source · release history
- Enables reusing Test Records for reruns, provided the record has more than one baseline and is not in Recording state. Rerunning existing security tests · Dec 2019 · source · release history
- Adds Create similar Test Run action in FAST Console to rerun security tests using an existing Test Record instead of recording a new one. Rerunning existing security tests · Dec 2019 · source · release history
Automated trigger configuration shipped Provides a console interface to configure automatic system reactions, such as blocking IPs or sending alerts, based on security events.
Also counts toward: Web management console, Outbound webhooks (the product notifies you)
release
- Enables setting triggers and notifications specifically for credential stuffing events. A new way to detect credential stuffing · Feb 2024 · source · release history
- Introduces Credential Stuffing detection capability to Wallarm node 4.10 for identifying compromised credential usage. A new way to detect credential stuffing · Feb 2024 · source · release history
- Adds support for receiving alerts on vulnerabilities found in applications, triggers generated by Wallarm, and service events like account changes or integration setting updates Wallarm API Security application for Splunk · Oct 2022 · source · release history
-
The Wallarm Node now uses port
443instead of port444to connect to the Wallarm Cloud. Wallarm Node 4.0 released and new SOC 2 Type II report · May 2022 · source · release history - Allows configuring conditions and filters on a Trigger to send messages to the Webhook URL. IBM QRadar and Micro Focus ArcSight integrations · Dec 2020 · source · release history
- Adds the Triggers section to the Wallarm Console UI for configuring automatic system reactions to events. Triggers · Sep 2020 · source · release history
Custom block page configuration shipped Allows configuring custom error pages and HTTP response codes when requests are blocked by the cyber tooling.
release
- Adds the ability to configure custom block pages returned alongside the 403 response for blocked malicious activity New Security Edge Features · Dec 2025 · source · release history
- Enables running tests without a predefined Test Policy by providing all parameters directly at runtime via CLI Schema-Based Testing Improvements · Nov 2025 · source · release history
- Customized Blocking Page now includes a new layout and additional debug data. Wallarm Node 4.0 released and new SOC 2 Type II report · May 2022 · source · release history
- Expands custom block page and HTTP response code configuration options Wallarm Node 2.16 released · Oct 2020 · source · release history
- Enables returning a custom error page and server code when an IP address is blocked. Wallarm Node 2.14 released · Mar 2020 · source · release history
API Vulnerability Scanner shipped Scans API assets to detect vulnerabilities and outdated software components, integrating with AASM for tracking and prioritization.
Shared capability: Vulnerability scanning
release
- Adds Bulk Import of Root Domains to quickly onboard multiple assets at once More Control and Accuracy in Scan Scope Configuration in API Attack Surface Management · May 2025 · source · release history
- Adds ability to add additional hosts for expanded scope definition More Control and Accuracy in Scan Scope Configuration in API Attack Surface Management · May 2025 · source · release history
- Introduces Scanning Profiles (pre-defined or custom) to match risk posture More Control and Accuracy in Scan Scope Configuration in API Attack Surface Management · May 2025 · source · release history
- General Availability of the API Vulnerability Scanner within Wallarm AASM Big Improvements to API Attack Surface Management · Feb 2025 · source · release history
- Expanded vulnerability detection covering approximately 2,500 widespread vulnerabilities and outdated software versions across web servers, frameworks, libraries, CMS platforms, plugins, programming languages, network services, and API gateways Big Improvements to API Attack Surface Management · Feb 2025 · source · release history
Endpoint Risk Scoring shipped Automatically calculates and displays risk scores for API endpoints based on criteria like sensitive data presence and parameter count.
release
- Enables blocking of detected API leaks via WAAP or Advanced API Security solution. Understanding your APIs from a hacker’s perspective · Dec 2023 · source · release history
- Adds customizable risk scoring capabilities within the API Discovery module to identify risky and attacked endpoints Introducing the Wallarm API Discovery Dashboard · Mar 2023 · source · release history
- Adds continuous scanning of public sources for API secrets leaks including public repositories, mobile apps, and Pastebin Introducing Proactive API Leak Management · Jan 2023 · source · release history
- Adds the ability to set custom rules for calculating endpoint risk scores in the Wallarm API Discovery module. Customization of endpoint risk score calculation · Dec 2022 · source · release history
- Adds automatic calculation of a risk score from 1 (low risk) to 10 (high risk) for each endpoint in the API inventory, based on criteria including sensitive data presence and parameter count. Stay on top of your riskiest endpoints with API Discovery · Dec 2022 · source · release history
Geographic and network source filtering shipped Allows configuring blocks or classifications based on IP geolocation (countries, data centers), Tor exit nodes, VPNs, and proxy servers.
Also counts toward: Web management console
release
- Adds the Malicious IPs feed source type for automated blocking of addresses identified in diverse Internet attacks Block bot-net activity with "Malicious IP" feeds · Sep 2023 · source · release history
- Introduces automatic updates for the Malicious IPs feed to keep most active bot-nets blocked without impacting regular users Block bot-net activity with "Malicious IP" feeds · Sep 2023 · source · release history
- Adds ability to block traffic originated from a specific country based on compliance requirements Blocking countries, Tor nodes, proxies, and data centers · Aug 2021 · source · release history
- Adds ability to block traffic from Tor exit nodes and popular proxy servers Blocking countries, Tor nodes, proxies, and data centers · Aug 2021 · source · release history
- Adds display of IP address source classification (countries, data centers, VPN, residential proxies) in the Wallarm Console Blocking countries, Tor nodes, proxies, and data centers · Aug 2021 · source · release history
Scan Schedule and Intensity Control shipped Enables global scan schedule management, auto-rescan per domain, and tenant/domain/IP-based rate limiting to control scan intensity.
Also counts toward: Scheduled jobs
release
- Wallarm AASM now allows configuring rate limits per tenant, domain, or IP via the Configure section to control scan intensity. Improved Control Over API Attack Surface Scans · Nov 2025 · source · release history
- Adds global scan schedule management with weekly, bi-weekly, or monthly options More Control and Accuracy in Scan Scope Configuration in API Attack Surface Management · May 2025 · source · release history
- Enables turning on/off the auto-rescan scheduler per domain in AASM More Control and Accuracy in Scan Scope Configuration in API Attack Surface Management · May 2025 · source · release history
docs
-
Copy View as Markdown Suggest changes Add Docs MCP Setup guide GraphQL API Protection Wallarm detects regular attacks (SQLi, RCE, etc. ) in GraphQL by default even under the basic WAAP subscription plan.
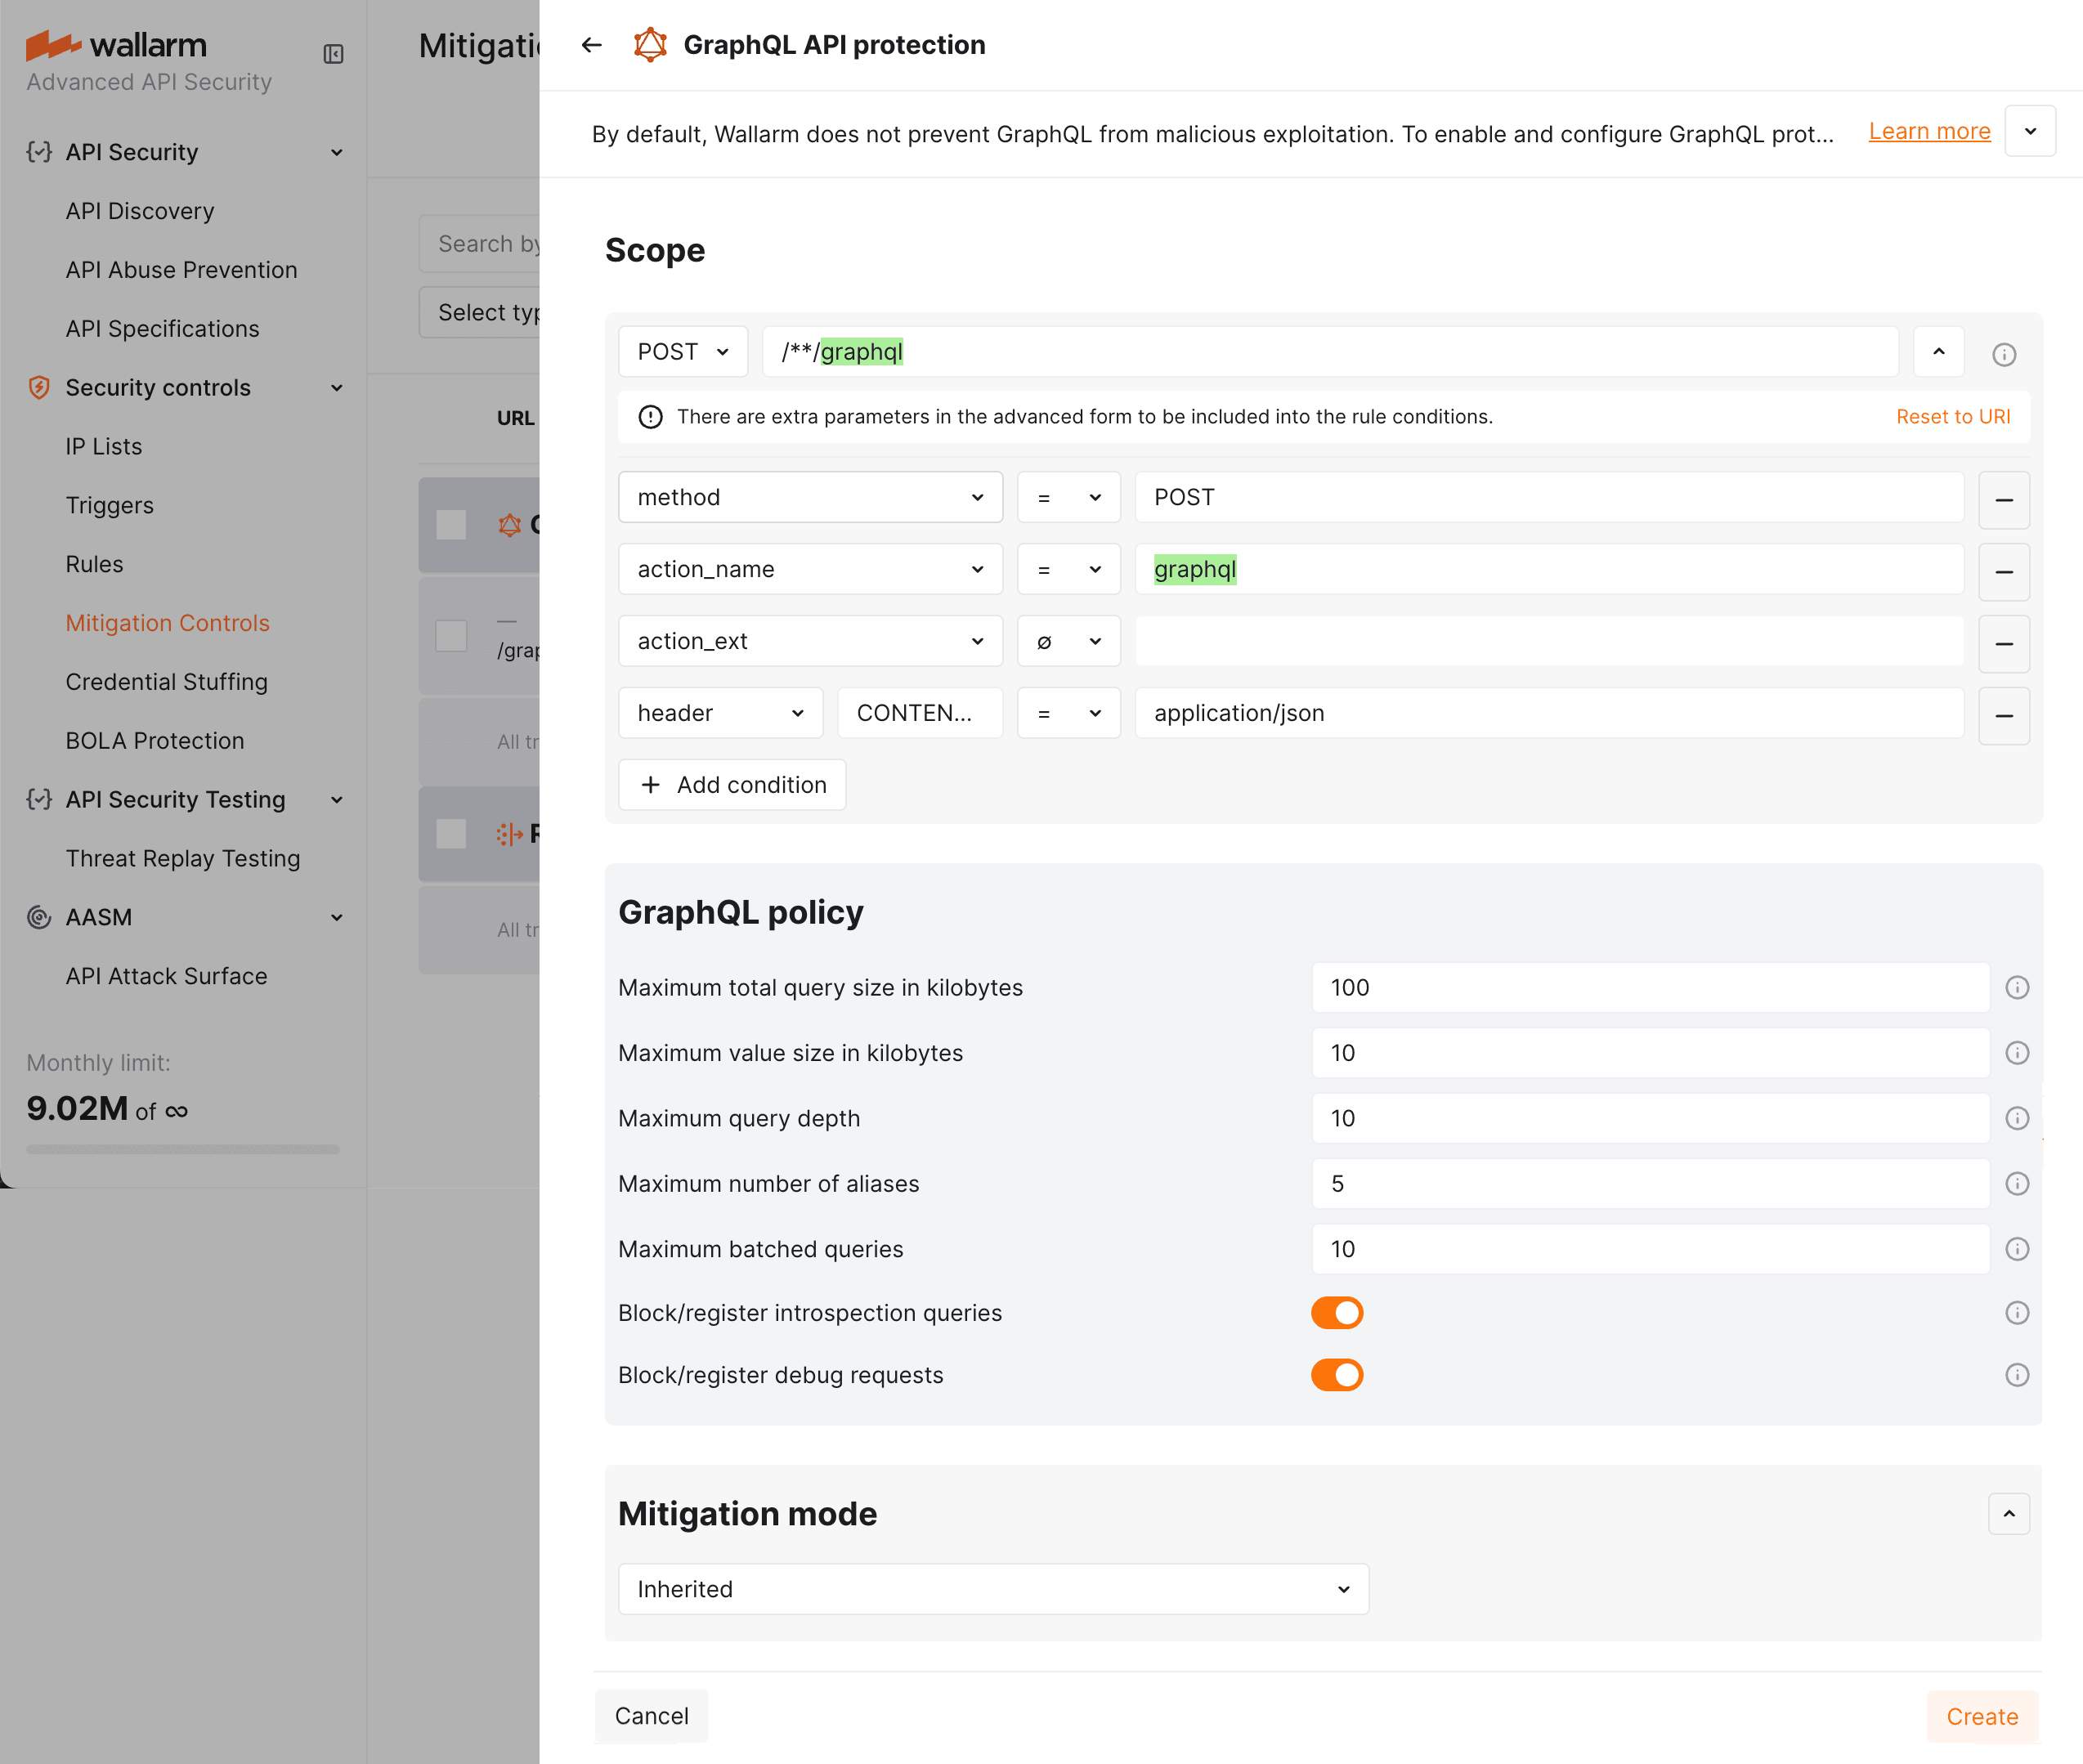 docs update · Aug 2026
· source
API and protocol discovery shipped Discovers APIs and protocols — including GraphQL and MCP — with version-specific Node requirements governing which protocols are available.
Also counts toward: GraphQL API support, gRPC API support
release
- Expanded dictionary for the DNS Enumeration technique used to discover exposed assets on the Scanner page. Enhanced DNS Enumeration technique and other detect updates · Jun 2020 · source · release history
-
Adds
gRPC/Protobuf parserto enable protection of gRPC-based APIs and microservices. Wallarm Node 2.14 released · Mar 2020 · source · release history -
Adds
gRPCprotocol support as the first cyber tooling to provide comprehensive protection for gRPC-based APIs Protecting gRPC applications and APIs · Mar 2020 · source · release history
docs
-
MCP discovery requires NGINX Node 6.12.0 or Native Node 0.25.0. For all protocols and their required Node versions, see Supported protocols GraphQL discovery requires NGINX Node 6.1.0 or Native Node 0.15.1.
docs update · Jul 2026
· source
API Inventory Authentication Classification shipped Classifies API endpoints based on authentication consistency (consistent, partial, missing) using production traffic analysis.
release
- Adds an unauthenticated endpoints filter to the inventory view to quickly list exposed APIs Know exactly how every API endpoint is authenticated (2026-05-05) · May 2026 · source · release history
- Adds consistent, partial, and missing authentication classifications for every API endpoint based on rolling 7-day production traffic analysis Know exactly how every API endpoint is authenticated (2026-05-05) · May 2026 · source · release history
docs
- used by each endpoint. This helps you find endpoints that lack proper authentication â the #1 API security risk. In addition to the recognized authentication types above, Wallarm ships a curated list of common authentication parameter names that are detected automatically â no configuration needed. seen Aug 2026 · source
example
-
Find APIs lacking consistent authentication in your inventory.
Open API Discovery inventory, apply filter 'Authentication status: Missing'.Know exactly how every API endpoint is authenticated (2026-05-05) · May 2026 · source
Vulnerability detail view shipped Redesigns the vulnerability details interface to show parameters, history timelines, and exploit examples for improved investigation.
release
- Adds toggle control to switch between the new grouped view and the legacy atomic view. Dynamic Grouping of Security Issues · Dec 2025 · source · release history
- Adds automatic grouping of similar security issues into single entries by title, type, risk level, and discovered-by fields. Dynamic Grouping of Security Issues · Dec 2025 · source · release history
- Enables expansion of issue groups to view individual items, affected resources, and statuses in one place. Dynamic Grouping of Security Issues · Dec 2025 · source · release history
- Redesigns the single vulnerability detail view to display parameters, history timeline, and exploit examples with improved readability Updated Vulnerabilities pages · May 2020 · source · release history
Report Export Capabilities shipped Exports detailed security reports in CSV, JSON, and DOCX formats with filtering options for hosts, ports, APIs, and risk levels.
Also counts toward: CSV data export, JSON data export
release
- Adds JSON report export for machine-readable integration 📢 Exciting Update: AASM reports download · Mar 2025 · source · release history
- Adds CSV report export grouped by Hosts, Ports, or APIs 📢 Exciting Update: AASM reports download · Mar 2025 · source · release history
- Adds DOCX report export for API Attack Surface Management with risk-level filtering 📢 Exciting Update: AASM reports download · Mar 2025 · source · release history
- CSV and JSON export capabilities for detailed security reports in the UI Big Improvements to API Attack Surface Management · Feb 2025 · source · release history
Identity provider integration shipped Enables integration with popular Identity Providers (IdP) such as Okta, Azure AD, and Auth0 for authentication.
release
- Adds the ability to align SSO provider groups with Wallarm roles for automatic user access assignment. Improved SSO Provisioning · Feb 2025 · source · release history
- Introduces User & Role-Based Filtering to attribute sessions to specific users and roles in API Sessions. Sensitive Business Flow Identification & User Attribution · Jan 2025 · source · release history
- Token-based Registration enables node registration via token on any supported platform. Wallarm Node 4.0 released and new SOC 2 Type II report · May 2022 · source · release history
- Enables integration with popular IdP providers including Okta, Azure AD, OneLogin, Auth0, and gSuite SAML authentication support · Aug 2020 · source · release history
Hit Grouping for Bot Analysis shipped Groups multiple hits from the same IP address into a single attack event to optimize bot and scanner analysis.
release
- Enables customizable detectors and thresholds for differentiating legitimate vs. malicious automated behaviors Protect your APIs against automated threats · Jul 2023 · source · release history
- Adds AI-driven anomaly detection for identifying malicious bot patterns in API requests and user sessions Protect your APIs against automated threats · Jul 2023 · source · release history
- Adds support for configuring the special trigger required to enable hit grouping in the Wallarm Console. Simplified attack grouping in the event list · Mar 2022 · source · release history
- Enables new event grouping method that consolidates hits from the same IP address into a single attack to optimize bot and scanner analysis. Simplified attack grouping in the event list · Mar 2022 · source · release history
Advanced rule conditions and triggers shipped Provides specialized triggers such as URI constructor for regex-based condition mapping, forced browsing protection, and brute force detection.
release
- Adds the Forced browsing trigger to protect against dirbusting using application 404 response codes. Simplified configuration of bruteforce protection · Nov 2021 · source · release history
- Adds the Bruteforce trigger for classic brute force protection based on incoming request counts per URI. Simplified configuration of bruteforce protection · Nov 2021 · source · release history
- Adds URI constructor form for rule conditions that accepts regular expressions and automatically converts request addresses into multiple conditions. URI constructor for rule conditions · Oct 2021 · source · release history
docs
- To review brute force default controls, in Wallarm Console â â To review BOLA default controls, in Wallarm Console â â To review generic enumeration default controls, in Wallarm Console â â To review forced browsing default controls, in Wallarm Console â â Proceed to Wallarm Console â of requests â… seen Aug 2026 · source
MCP Server Protection and Discovery shipped Discovers exposed MCP servers and enforces granular access controls for tool usage.
release
- Adds visibility into exposed MCP servers, including their tools, resources, authentication status, and any sensitive data detected. Introducing a New API Discovery Dashboard (2026-10-13) · Oct 2026 · source · release history
- Adds MCP Protection feature to Wallarm Advanced API Security for discovering exposed MCP servers, tools, and resources Introducing MCP Protection (2026-05-12) · May 2026 · source · release history
example
-
Investigate exposed MCP servers and check whether they require authentication or expose sensitive data.
In the Wallarm console, go to Dashboards → Discovered inventory, then scroll to the MCP servers section to review each server's tools, resources, authentication status, and sensitive data exposure.Introducing a New API Discovery Dashboard (2026-10-13) · Oct 2026 · source
Triggered payload identification shipped Marks the specific payload within a multi-payload request that triggered an incident, distinguishing it from other payloads in the same request that did not hit a vulnerability.
release
-
Marks the specific payload within a request that triggered the incident, distinguishing it from other payloads in the same request that did not hit a vulnerability.
Introducing the New Incidents Interface (2026-09-29) · Sep 2026
· source
· release history
- Marks the specific payload within a multi-payload request that triggered the incident, so analysts do not have to identify which payload caused the damage. announced · Sep 2026 · source · release history
- Adds Block Compromised Sessions option to Mitigation Controls for terminating malicious API sessions Granular Control to Stop Attacks Without Disrupting Legitimate Users · Sep 2025 · source · release history
MCP Server Protection documented Discovers exposed Model Context Protocol (MCP) servers and provides granular access controls, input schema enforcement, and session analysis for tool usage.
Also counts toward: Web management console
docs
- 0.25.0+. To analyze MCP servers that stream their responses as Server-Sent Events (SSE, Content-type: text/event-stream ), 6.13.0+ is required. You can define general API Discovery settings in Wallarm Console â â â â â See details here â seen Aug 2026 · source
-
Security Issues Business flow â AI/LLM servers alongside their primitives â tools, resources, and prompts. â ACL policies, request verification, and tool input schema enforcement.
docs update · Aug 2026
· source
-
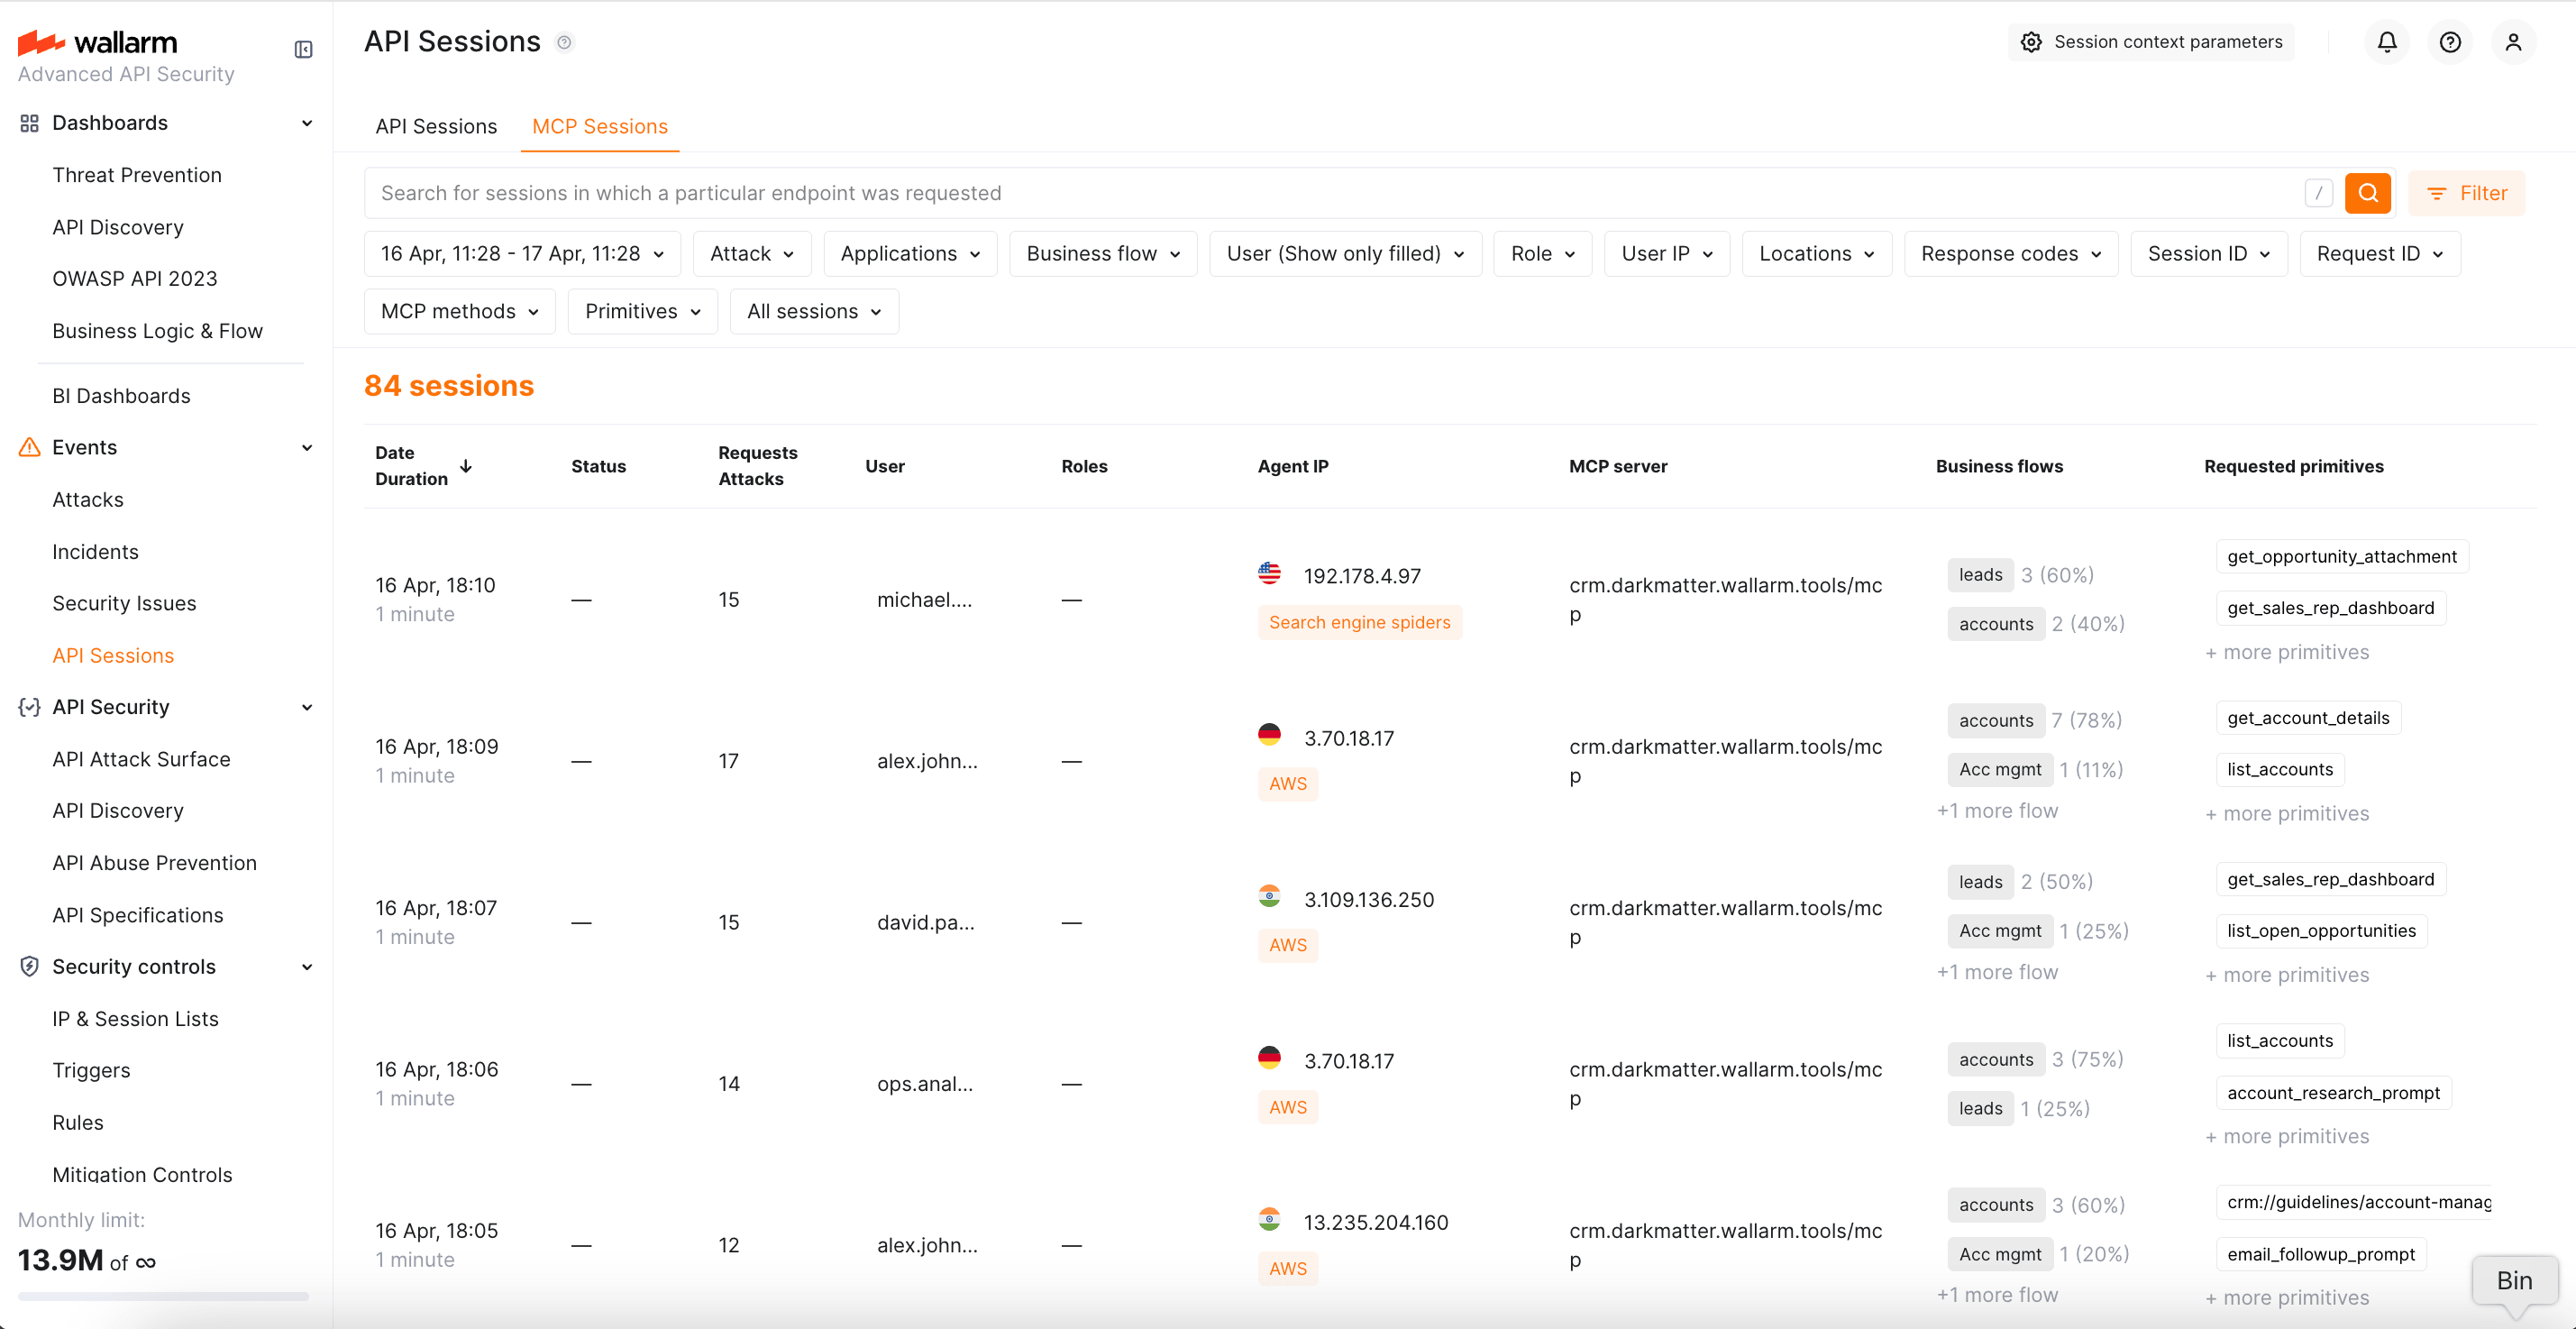
tab in Wallarm Console â header â a standard MCP protocol header that identifies a session. â the host and path of the MCP server endpoint â the value of the â extracted from session context if â MCP methods called during the session ( â names of tools, resources, or prompts accessed during the session…
 docs update · Aug 2026
· source
Passive Traffic Mirroring shipped Mirrors out-of-band traffic to nodes using VXLAN or Geneve encapsulation for API discovery and detection without latency.
release
- Enables mirroring of out-of-band traffic to Wallarm Nodes for API Discovery, Session analysis, and Attack detection without adding latency AWS VPC Traffic Mirroring Support Is Here (2026-04-08) · Apr 2026 · source · release history
-
Adds
VXLANencapsulation support to mirror traffic from AWS Elastic Network Interfaces (ENIs) AWS VPC Traffic Mirroring Support Is Here (2026-04-08) · Apr 2026 · source · release history -
Adds Geneve
-encapsulatedtraffic support to the TCP traffic analysis engine for AWS VPC Traffic Mirroring AWS VPC Traffic Mirroring Support Is Here (2026-04-08) · Apr 2026 · source · release history
Advanced Sensitive Data Detection shipped Identifies sensitive data in API responses using custom context words and 40+ out-of-the-box detection patterns.
release
- Adds a new Azure APIM connector for synchronous and asynchronous API traffic analysis Deploy Wallarm With Azure APIM, Apigee, and Akamai · Sep 2025 · source · release history
- Enables custom sensitive data detection using context words without regex Product Announcement: Sensitive Data Detection Enhancements · Oct 2024 · source · release history
- Adds 40+ out-of-the-box detections for sensitive data (credentials, financial, personal, technical) in the API Discovery module Product Announcement: Sensitive Data Detection Enhancements · Oct 2024 · source · release history
Risk Analysis and Prioritization shipped Provides historical and resolution risk analysis with an expanded 5-level risk model to prioritize security issues.
release
- Resolution Risk Analysis chart visualizing the speed of issue resolution over time Big Improvements to API Attack Surface Management · Feb 2025 · source · release history
- Upgrade from a 3-level to a 5-level risk model for prioritization Big Improvements to API Attack Surface Management · Feb 2025 · source · release history
- Historical Risk Analysis chart tracking monthly vulnerability trends by risk level Big Improvements to API Attack Surface Management · Feb 2025 · source · release history
GraphQL Protection and Parsing shipped Provides internal GraphQL parsing, parameter extraction for session context, and granular rule application for specific request components.
Also counts toward: GraphQL API support
release
- Enables extraction of GraphQL request parameter values for use as Session Context Parameters Full-Fledged GraphQL Parser · Feb 2025 · source · release history
- Includes a new internal GraphQL parser in Wallarm node version 5.3.0+ Full-Fledged GraphQL Parser · Feb 2025 · source · release history
- Allows application of granular protection rules to specific GraphQL request components (arguments, directives, variables) Full-Fledged GraphQL Parser · Feb 2025 · source · release history
Native Node Deployment shipped Offers an NGINX-independent deployment option for Wallarm connectors, including Docker and Kubernetes support.
Also counts toward: Kubernetes-native deployment
release
- Supports securing APIs through Kong API Gateway and Envoy via the Native Node Introducing Native Node for Streamlined Connector Deployment · Oct 2024 · source · release history
- Adds the Native Node deployment option for Wallarm connectors that operates independently of NGINX Introducing Native Node for Streamlined Connector Deployment · Oct 2024 · source · release history
- Releases deployment artifacts for Native Node including an all-in-one installer, Docker image, and Helm chart Introducing Native Node for Streamlined Connector Deployment · Oct 2024 · source · release history
API Edge Filtering Infrastructure shipped Provides hosted, geographically distributed infrastructure for low-latency API traffic filtering and real-time metrics.
release
- Hosted, managed infrastructure for API edge filtering Product Announcement: Security Edge Service · Oct 2024 · source · release history
- Geographically distributed nodes for minimal latency Product Announcement: Security Edge Service · Oct 2024 · source · release history
- Full access to logs, events, and real-time traffic metrics Product Announcement: Security Edge Service · Oct 2024 · source · release history
API Attack Surface Visibility shipped Surfaces endpoints with the highest proportion of attack traffic and identifies unauthenticated or shadow endpoints to help teams prioritize remediation by actual threat signal.
release
- Surfaces endpoints with the highest proportion of attack traffic so teams can prioritize remediation by actual threat signal. Introducing a New API Discovery Dashboard (2026-10-13) · Oct 2026 · source · release history
example
-
Navigate to the new dashboard to review your full API attack surface and identify unauthenticated or shadow endpoints that need immediate attention.
In the Wallarm console, go to Dashboards → Discovered inventory to view internet-exposed APIs, unauthenticated endpoints, shadow and zombie APIs, and open security issues.announced · Oct 2026 · source
AI Session Isolation and Control shipped Manages untrusted LLM sessions with kill switches and enforces permissions via agent behavior certificates.
release
- Adds session kill switch by user subject or W3C trace ID, enforced at the kernel, for untrusted LLM sessions Introducing the Wallarm AI Control Platform (2026-06-04) · Jun 2026 · source · release history
- Adds agent behavior certificates to pin and enforce permissions for each agent Introducing the Wallarm AI Control Platform (2026-06-04) · Jun 2026 · source · release history
AWS Asset Relationship Graphing shipped Provides a live relationship graph for discovered infrastructure assets showing blast-radius traversal and attack paths.
release
- Adds live relationship graph with blast-radius traversal and attack-path analysis for discovered infrastructure assets Introducing the Wallarm AI Control Platform (2026-06-04) · Jun 2026 · source · release history
docs
- â full operational surface: API discovery, attack monitoring, rules, integrations, mitigation controls, sessions, and more. (AWS-only) â cross-account AWS asset discovery and the relationship graph (when active on the subscription). â vulnerability findings from passive detection and AASM. seen Aug 2026 · source
Field-Level Drift Detection shipped Detects field-level drift between scans with CloudTrail attribution on every asset.
release
- Adds field-level drift detection between scans with CloudTrail creator attribution on every asset Introducing the Wallarm AI Control Platform (2026-06-04) · Jun 2026 · source · release history
docs
- capabilities for AWS â continuous asset inventory, drift detection, and exposure surfacing across your cloud estate. Access is read-only â Infrastructure Discovery never modifies your cloud resources. instances â US and EU. seen Aug 2026 · source
Infrastructure Asset Discovery shipped Continuously inventories AWS assets across accounts and regions via IAM role assumption.
release
- Adds Infrastructure Discovery to continuously inventory AWS assets (EC2, VPC, EKS, Lambda, API Gateway, IAM, Bedrock) across accounts and regions via IAM role assumption Introducing the Wallarm AI Control Platform (2026-06-04) · Jun 2026 · source · release history
docs
- capabilities for AWS â continuous asset inventory, drift detection, and exposure surfacing across your cloud estate. Access is read-only â Infrastructure Discovery never modifies your cloud resources. instances â US and EU. seen Aug 2026 · source
Automated Session Configuration shipped Provides automatic parameter suggestions when configuring API sessions based on existing discovery data.
release
- Adds automatic parameter suggestions when configuring API sessions, leveraging existing API Discovery data to reduce setup time. Faster, Smarter API Session Setup (Now With Recommendations) (2026-02-04) · Feb 2026 · source · release history
example
-
Use the new UI recommendations to configure a session for an unfamiliar third-party API without manual parameter mapping.
In the Wallarm console, go to API Sessions > New Session and review the auto-suggested parameters before saving.Faster, Smarter API Session Setup (Now With Recommendations) (2026-02-04) · Feb 2026 · source
Connector Response Analysis shipped Updates existing connectors to parse and analyze API responses in addition to requests.
release
- Updates the Apigee connector to parse and analyze API responses in addition to requests Deploy Wallarm With Azure APIM, Apigee, and Akamai · Sep 2025 · source · release history
- Updates the Akamai connector to parse and analyze API responses in addition to requests Deploy Wallarm With Azure APIM, Apigee, and Akamai · Sep 2025 · source · release history
Session Anomaly Detection shipped Uses machine learning detectors to identify Account Takeover (ATO) attacks via session or IP rotation.
Also counts toward: ML-based detection
release
- Adds Session Rotation machine learning detector to identify ATO attacks where attackers rotate session IDs while using a single IP address. Improved Detection of Account Takeover (ATO) Attacks · Aug 2025 · source · release history
- Adds IP Rotation machine learning detector to identify ATO attacks where attackers use a pool of IPs within a single stable session. Improved Detection of Account Takeover (ATO) Attacks · Aug 2025 · source · release history
SAP API Management integration shipped Enables securing APIs managed through SAP Integration Suite API Management.
release
- Adds a native integration with IBM DataPower API Gateway for forwarding API traffic directly to Wallarm nodes Wallarm Now Natively Supports IBM DataPower API Gateway · May 2025 · source · release history
docs
- SAP API Management Secure APIs managed with SAP Integration Suite API Management seen Oct 2026 · source
Sensitive Business Flow Tagging shipped Allows automatic and manual identification and tagging of critical endpoints and business flows for focused protection.
release
- Enables customizable manual tagging of Sensitive Business Flows to meet unique business requirements. Sensitive Business Flow Identification & User Attribution · Jan 2025 · source · release history
- Adds automatic identification and tagging of critical endpoints for authentication, billing, and account management in API Discovery & API Sessions. Sensitive Business Flow Identification & User Attribution · Jan 2025 · source · release history
Bot Sensitivity and Behavior Analysis shipped Provides granular controls for bot sensitivity and domain-scoped behavioral analysis to manage API abuse.
release
- Wallarm updates API abuse management with granular bot sensitivity controls and domain-scoped behavioral analysis capabilities. Enhanced API Abuse Security Profiles · May 2024 · source · release history
- The Tolerance parameter is replaced by Sensitivity levels, requiring configuration updates in existing profiles. Enhanced API Abuse Security Profiles · May 2024 · source · release history
OpenAPI Specification Enforcement shipped Allows uploading and enforcing OpenAPI specifications to detect and block violations such as unknown parameters, missing required fields, or invalid data types.
release
- Requires Wallarm node version 4.10.4 or above and an Advanced API Security subscription. Protect your APIs with specification enforcement · May 2024 · source · release history
- Enables upload and enforcement of OpenAPI specifications to detect and block violations such as unknown parameters, missing required fields, invalid data types, incorrect endpoints, and wrong authentication methods. Protect your APIs with specification enforcement · May 2024 · source · release history
NIST CSF 2.0 Compliance View shipped Provides dashboards and insights aligned with NIST Cybersecurity Framework version 2.0 for security posture assessment.
release
- Adds NIST Cybersecurity Framework version 2.0 (CSF 2.0) dashboards to the Wallarm platform for high-level overview of security controls. Evaluate your security posture with NIST CSF dashboards · Feb 2024 · source · release history
- Provides comprehensive insights into API and application security posture, guiding teams through identifying, protecting, detecting, and responding to threats. Evaluate your security posture with NIST CSF dashboards · Feb 2024 · source · release history
Insecure Direct Object Reference (IDOR) Protection shipped Automatically detects endpoints passing object IDs and creates triggers to protect against Insecure Direct Object References.
release
- Integrates Wallarm API Discovery module to identify endpoints passing object IDs Automatic protection from BOLA attacks · Dec 2022 · source · release history
- Adds automatic trigger creation for BOLA (Insecure Direct Object References) attack protection Automatic protection from BOLA attacks · Dec 2022 · source · release history
Kubernetes Sidecar Injection shipped Enables automatic injection of a protection sidecar into Kubernetes pods with annotation and label-based configuration.
Also counts toward: Kubernetes-native deployment
release
- Enables automatic injection of the Sidecar into Kubernetes Pods Enhanced Wallarm Sidecar proxy solution · Sep 2022 · source · release history
- Introduces annotation and label-based configuration to secure application pods with minimum setup Enhanced Wallarm Sidecar proxy solution · Sep 2022 · source · release history
System status monitoring and visibility shipped Provides real-time availability data for the console via a public status page and command-line monitoring tools without support tickets.
Also counts toward: Command-line interface
release
-
Publicly accessible status page at
status.wallarm.comdisplaying live and historical availability data Status page available at status.wallarm.com · Mar 2021 · source · release history
example
-
Monitor Wallarm Console availability across all clouds without needing to open a support ticket.
https://status.wallarm.comStatus page available at status.wallarm.com · Mar 2021 · source
WAF node monitoring statistics shipped Provides new statistical parameters for monitoring the performance and status of WAF nodes.
release
- Introduces new statistical parameters for monitoring the WAF node Wallarm Node 2.16 released · Oct 2020 · source · release history
example
-
Monitor Wallarm Console availability across all clouds without needing to open a support ticket.
https://status.wallarm.comStatus page available at status.wallarm.com · Mar 2021 · source
Node version visibility shipped Displays version information for WAF node components and configuration files directly in the console.
release
-
Displays
LOMfile andproton.dbversion information within the WAF node card in the Wallarm Console UI WAF Component Versions in Wallarm Console · Oct 2020 · source · release history - Displays WAF node component versions directly in the Wallarm Console Wallarm Node 2.16 released · Oct 2020 · source · release history
Auto-scaling infrastructure support shipped Supports native auto-scaling on AWS and GCP environments for the cyber tooling nodes.
release
-
Adds
BUILD_IDenvironment variable support to the FAST node configuration to enable running a single instance across multiple concurrent CI/CD pipelines Support of Parallel CI Pipelines · Apr 2020 · source · release history - Wallarm Nodes now natively support auto-scaling in AWS and GCP. Auto-scaling of nodes in AWS, GCP, Azure · Aug 2019 · source · release history
API Exposure Detection documented Identifies undocumented, deprecated, or otherwise exposed API endpoints by analyzing legitimate traffic patterns and comparing them against known specifications.
docs
- â Find undocumented endpoints (in traffic but not in any of your specs). â Find deprecated endpoints that still handle traffic (removed from spec but still in use). seen Aug 2026 · source
- and discovery starts over from scratch â past parameter information and history are not recovered. â daily or hourly summaries of new and changed endpoints, delivered to your account email and any additional addresses. seen Aug 2026 · source
Crown Jewel Management shipped Allows pinning and unpining crown jewels via the console UI to dynamically reorganize path scoring.
Also counts toward: Web management console
release
-
Enables pinning and unpining
crown jewelsvia the console UI to dynamically reorganize path scoring and priority rankings. See how an attacker would reach your critical AWS assets (2026-07-30) · Jul 2026 · source · release history
AI Workload Instrumentation shipped Instruments AI workloads at runtime using a Kubernetes DaemonSet and mutating admission webhook.
Also counts toward: Kubernetes-native deployment
release
- Adds AI Hypervisor, a Kubernetes DaemonSet using a mutating admission webhook to instrument AI workloads at runtime without code changes Introducing the Wallarm AI Control Platform (2026-06-04) · Jun 2026 · source · release history
Compliance Reporting for AI Act shipped Generates continuous compliance reports aligned with EU AI Act requirements.
release
- Generates continuous compliance reports (AI inventory, coverage heatmap, session logs, PII egress records) aligned with EU AI Act requirements Introducing the Wallarm AI Control Platform (2026-06-04) · Jun 2026 · source · release history
Asset Discovery via Network Range shipped Enables scanning single IPs, subnets, and CIDR ranges to discover hidden internet-facing assets.
release
- Scan single IPs, subnets, and CIDR ranges in addition to domains via the AASM Configuration screen AASM Updates — broader visibility, faster validation, clearer reporting (2026-03-26) · Mar 2026 · source · release history
Asset Remediation Validation shipped Allows rescanning single assets directly from the per-asset view to validate remediation.
release
- Rescan a single asset directly from the per-asset view to validate remediation AASM Updates — broader visibility, faster validation, clearer reporting (2026-03-26) · Mar 2026 · source · release history
API Schema Input Support shipped Allows uploading RAML files for schema-based testing with automatic conversion to OpenAPI.
release
- Adds RAML file upload as an input source for Schema-Based Testing with automatic conversion to OpenAPI API Security Testing Keeps Getting Better (2026-02-16) · Feb 2026 · source · release history
mTLS Authentication Support shipped Enables testing of APIs that require mutual TLS authentication.
release
- Adds support for testing APIs that require mTLS authentication API Security Testing Keeps Getting Better (2026-02-16) · Feb 2026 · source · release history
API Access Control List (ACL) Management shipped Allows creating and managing ACLs to define which IP addresses can access specific hosts and locations of APIs.
release
- Adds support for creating and managing Access Control Lists (ACLs) to define which IP addresses can access specific hosts and locations of APIs New Security Edge Features · Dec 2025 · source · release history
Inline Node Response Caching shipped Supports content caching rules to define how inline nodes store and reuse responses from specific hosts and locations.
release
- Adds support for content caching rules defining how Inline nodes store and reuse responses from specific hosts and locations New Security Edge Features · Dec 2025 · source · release history
OWASP API2 Authentication Checks shipped Adds checks for broken authentication vulnerabilities, including missing auth enforcement and JWT tampering, in OpenAPI-based scans.
release
- Adds OWASP API2 (Broken Authentication) checks in OpenAPI-based scans to uncover missing auth enforcement, weak token validation, JWT tampering, and exposed credentials in query strings Schema-Based Testing Improvements · Nov 2025 · source · release history
Facet-Based Filtering shipped Adds filtering via specific facets with wildcard and regex support across system pages.
release
-
Adds filtering via facets (
region,host,request_method,nginx_status,upstream_status,remote_addr,upstream_addr,request_uri,req_id) with wildcard and regex support Expanded Security Edge Observability: Inline Node Logs Now in the Telemetry Portal · Oct 2025 · source · release history
Telemetry and Log Visualization shipped Provides a new dashboard for viewing access and error logs from Inline nodes.
release
- Adds a new Telemetry Portal → Wallarm → Inline Node Logs dashboard for viewing access and error logs Expanded Security Edge Observability: Inline Node Logs Now in the Telemetry Portal · Oct 2025 · source · release history
Mitigation Control Configuration shipped Streamlines custom attack response configuration via a new UI, including blocking compromised sessions.
release
- Mitigation controls available on node 6.5.x+ streamline custom attack response configuration via a new UI. Faster, Easier Custom Response Options for Attacks · Sep 2025 · source · release history
Automated Security Issue Lifecycle Management shipped Automatically closes or reopens discovered security issues after each scan based on changes in findings.
release
- AASM now automatically closes or reopens discovered Security Issues after each scan when changes are detected in the findings Automated Security Issue Rechecking in AASM · Jul 2025 · source · release history
AI-Powered CVE Classification shipped Uses OpenAI LLMs to automatically categorize and classify detected vulnerabilities.
release
- AI-powered CVE classification using OpenAI LLMs to automatically categorize detected vulnerabilities Big Improvements to API Attack Surface Management · Feb 2025 · source · release history
Vulnerability Intelligence Enrichment shipped Enriches detected vulnerabilities with public exploit availability, in-the-wild status, and EPSS ranking data.
release
- Vulnerability Intelligence Enrichment providing public exploit availability, in-the-wild exploitation status, ransomware campaign usage, and EPSS ranking for detected issues Big Improvements to API Attack Surface Management · Feb 2025 · source · release history
WAAP Coverage Detection shipped Detects other Web Application and API Protection solutions operating on open ports to identify security coverage gaps.
release
- Adds Detection of WAAP solutions for each open port to identify coverage gaps on non-standard ports Improvements to API Attack Surface Management · Sep 2024 · source · release history
WAAP Score Evaluation Reporting shipped Generates reports detailing attack detection types and false-positive rates for security posture evaluation.
release
- Enables download of a WAAP Score Evaluation report containing attack detection types and false-positive rates Improvements to API Attack Surface Management · Sep 2024 · source · release history
JavaScript Polyfill Malicious Domain Detection shipped Detects static imports of JavaScript code from known malicious domains involved in specific supply chain campaigns.
Also counts toward: Scripting language support
release
- Detects static imports of JavaScript code from the polyfill.io domain and other malicious domains involved in this campaign: kuurza[.]com, googie-anaiytics[.]com, bootcss[.]com, macoms[.]lanewcrbpc[.]com, polyfill[.]io, bootcdn[.]net, staticfile[.]net, unionadjs[.]com, xhsbpza[.]com Malicious JavaScript injection via supply chain attack (polyfill.io) · Jul 2024 · source · release history
OOB Attack Detection shipped Adds detection capabilities for Out-of-Band (OOB/OAST) attack techniques.
release
- Adds new indicators of Out-of-Band (OOB/OAST) attack techniques to the product Wallarm Detection Updates · Mar 2024 · source · release history
Attack outcome visibility shipped Displays explicit status (blocked or reached application) for malicious requests in the console to clarify interception results.
release
- Malicious requests in the console now display an explicit status indicating whether they were blocked or reached the application, replacing the previous reliance on HTTP status codes (e.g. 403). Action status for every malicious request · Apr 2019 · source · release history
Cross-Platform Log Forwarding documented Forwards security events to external platforms such as Splunk, Datadog, QRadar, and ArcSight via Fluentd or direct integration.
Also counts toward: SIEM forwarding
docs
- Wallarm â Fluentd â Datadog Wallarm â Logstash â Datadog Wallarm â Fluentd â IBM QRadar Wallarm â Fluentd â Splunk Enterprise Wallarm â Fluentd â Micro Focus ArcSight Logger Wallarm â Fluentd â Datadog Wallarm â Logstash â IBM QRadar Wallarm â Logstash â Splunk Enterprise Wallarm â… seen Aug 2026 · source
Incident Investigation Workflow documented Provides a workflow to navigate from an incident directly to request details and API sessions for investigation.
Also counts toward: Web management console
docs
- To perform this analysis, in Wallarm Console â , open the attack, switch to the Requests tab, and select a request. In the request details, open the field menu and select Investigate this attack in API Sessions . , access the incident and then the request details, and click . seen Aug 2026 · source
Sensitive Data Detection Configuration documented Allows modification of default sensitive data patterns and adding custom ones in the console.
Also counts toward: User-defined detection rules, Web management console
docs
- â â - each pattern defines specific sensitive data and settings for its search. API Discovery goes with the set of default patterns. You can modify default patterns and add your own in Wallarm Console â â â seen Aug 2026 · source
Session Grouping Configuration documented Enables manual addition of session grouping keys for request and response bodies, queries, and properties.
Also counts toward: Web management console
docs
- Go to Wallarm Console â â To add session grouping keys manually, go to Wallarm Console â â RESPONSE â BODY JSON â PROPERTY â token REQUEST â QUERY â token REQUEST â BODY â JSON â PROPERTY â token RESPONSE â BODY â JSON â PROPERTY â token REQUEST â QUERY â token REQUEST â BODY… seen Aug 2026 · source
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
2 commands for Wallarm, each with where it came from. This tool has no source analysis yet, so there is no option reference and no captured run beside them.
No command matches.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for Wallarm, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Wallarm puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Website history
wallarm.com, every changeWallarm's home page as it looked each month from September 2021 to July 2026: 11 renders, 8 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Releases
130 entries
No entries match these filters.
- October 20262
- September 20264
- August 20265
- July 20265
- June 20261
- May 20262
- April 20261
- March 20262
- February 20263
- January 20262
- December 20252
- November 20252
- October 20252
- September 20254
- August 20252
- July 20251
- June 20251
- May 20252
- March 20251
- February 20254
- January 20251
- October 20243
- September 20242
- August 20241
- July 20243
- May 20243
- April 20242
- March 20241
- February 20243
- January 20242
- December 20231
- October 20232
- September 20232
- August 20231
- July 20235
- May 20232
- April 20232
- March 20233
- January 20231
- December 20223
- November 20222
- October 20221
- September 20222
- August 20222
- July 20222
- May 20221
- March 20221
- February 20221
- November 20212
- October 20211
- August 20212
- March 20212
- December 20201
- November 20201
- October 20202
- September 20202
- August 20202
- June 20201
- May 20201
- April 20201
- March 20202
- December 20194
- October 20191
- August 20191
- April 20191
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →