Aikido Security
🚀External Network Pentesting: test your perimeter before someone else does commercialThe section your link pointed to isn't on Aikido Security's page any more, so we've brought you to the top.
Aikido Security is a developer-focused application security platform that scans code, dependencies, containers, and cloud infrastructure to detect and help fix vulnerabilities.
# Place a .aikido file at the root of your repository with custom context
echo 'We use our internal wrapper `safe_query()` instead of raw DB calls.' > .aikido
Summary
Aikido Security is a commercial appsec platform that scans code, cloud accounts, containers, and virtual machines, then brings the resulting findings into one place for triage and remediation. It runs as a SaaSSaaSSoftware delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally. service, with a broker option for connecting on-premises sources like GitHub Enterprise Server, and it plugs into pull requests, IDEs, Slack, and task trackers so fixes surface where developers already work. It is aimed at application security and development teams who need vulnerability management, container and Kubernetes checks, and continuous automated pentesting without stitching together separate tools for each layer. It sits in the appsec space, covering scanning, autofix, and runtime protection under one product rather than one narrow niche. Launched in 2022 and still shipping frequently, with 34 tracked releases and its last one 37 days ago, it looks actively maintained.
Aikido Security is a developer-focused application security platform that scans code, dependencies, containers, and cloud infrastructure to detect and help fix vulnerabilities.
How Aikido Security helps
Which of my open-source dependencies actually get executed by code that runs, versus sitting unused in the tree?
traces reachability from entry points into the dependency graph and flags only the vulnerable packages whose code path is actually invoked, so triage starts with what matters
Which container images running in my live Kubernetes clusters have known vulnerabilities right now?
continuously monitors images deployed in the cluster rather than just the registry, so a clean image that later gets a disclosed flaw is caught while it is running
Is this dependency upgrade going to break my build before I merge it?
analyzes the upgrade for code-breaking changes and surfaces the impact alongside the fix, before the version bump is applied
Which of my cloud subscriptions are exposed to a misconfiguration, including ones spun up after I connected my account?
auto-discovers subscriptions and groups under a connected account, both existing and future, so new environments inherit scanning without a manual reconnect
Has a specific vulnerability actually been fixed, without re-running an entire pentest against the whole application?
re-tests the single finding in isolation and reports whether that one issue is resolved
Can an AI coding agent check my code for security issues without sending the source out of my machine?
runs the analysis locally against the code and reports risks and fixes without transmitting code or data to the cloud
Languages
Features
Built from Aikido Security's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- Aikido Security covers 5 of the 8 vulnerability assessment methods capabilities we track.
What Aikido Security offers you
- REST API8
- Scripting language support4
- Built-in AI assistant2
- ML-based detection2
- Agent-based deployment1
- CI/CD pipeline integration1
- Import from a competing product1
- Kubernetes-native deployment1
- MCP server1
- Multi-factor authentication1
- Natural-language query1
- Outbound webhooks (the product notifies you)1
- Python scripting support1
- Scheduled jobs1
- Scripting API1
- Self-hosted deployment1
- SIEM forwarding1
- Ticketing integration1
- User-defined detection rules1
No capabilities match.
Static application security testing 4 features Vulnerability assessment methods since 2026
Data Exposure Audit (DSPM) shipped Traces how sensitive data flows through source code to detect API over-exposure, unsafe logging, credential leakage, and other data mishandling issues.
Shared capability: Static application security testing
release 24 total
- Adds Sensitive Data information to DSPM. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
-
New Data Exposure Audit capability uses LLM agents to trace sensitive data from sources (request bodies, uploads, DB reads, config, app logic) into sinks (logs, third-party APIs, LLM prompts, caches, queues, storage) — all from already-connected repos.
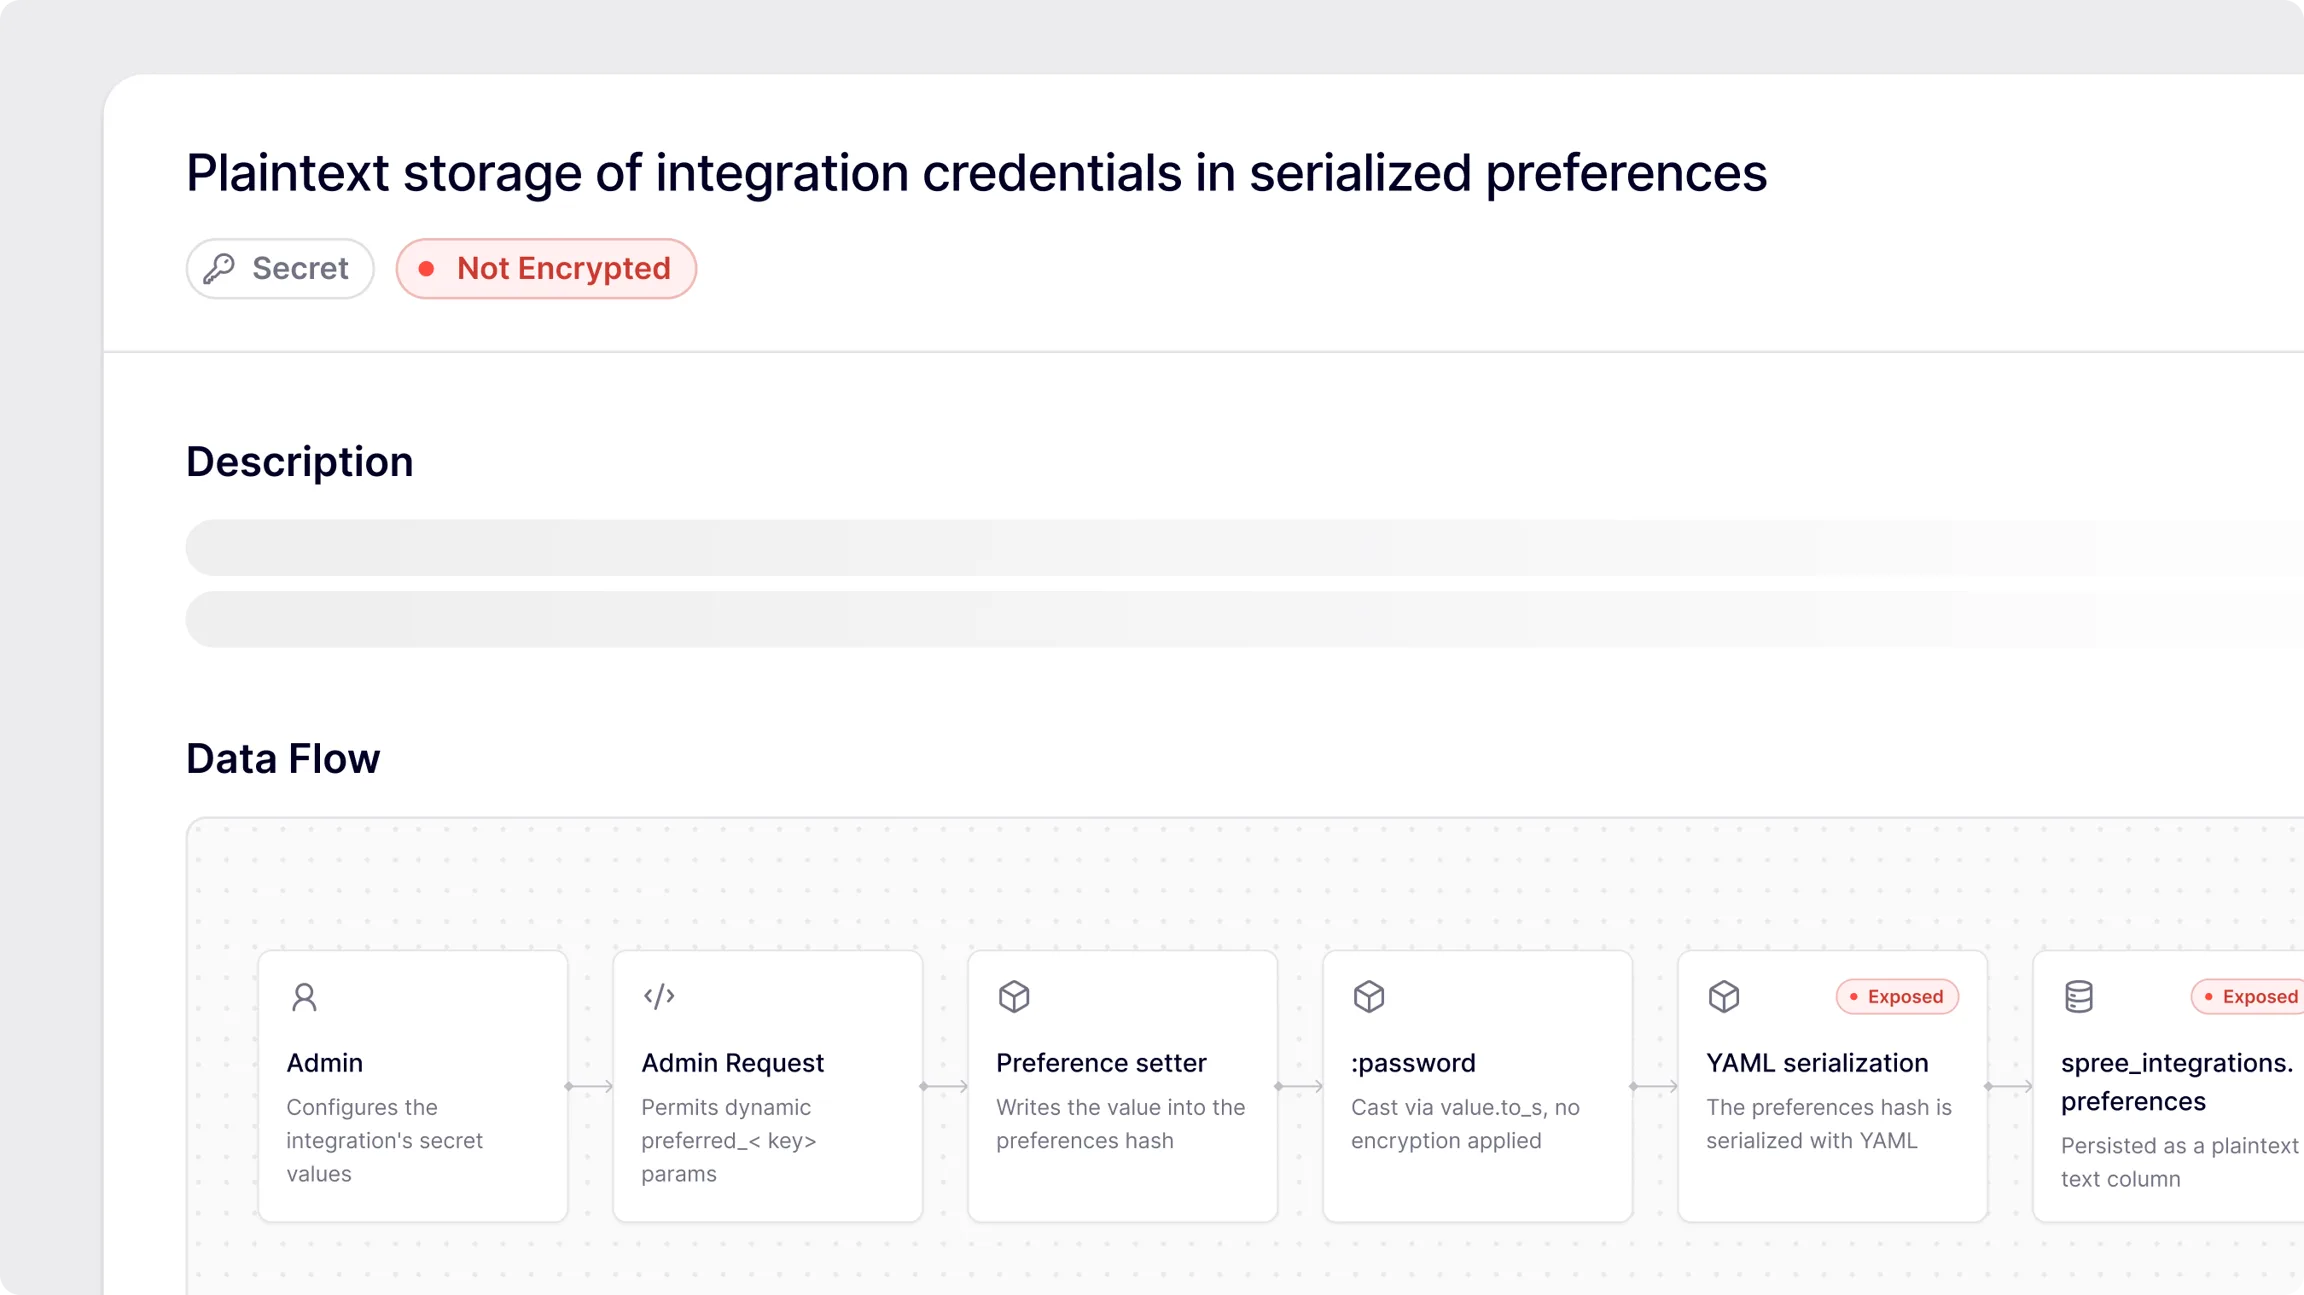 🚀DSPM: Find data exposure risks without connecting your data stores · seen Aug 2026
· source
· release history
- Detects incomplete deletion — delete flows that leave downstream records, caches, and related stores intact, including shadow copies in staging and snapshots. 🚀 DSPM: Find data exposure risks without connecting your data stores · seen Aug 2026 · source · release history
- Detects credentials in URLs — tokens and API keys in query strings, redirects, and clone URLs that may be captured by logs, proxies, or browser history. 🚀 DSPM: Find data exposure risks without connecting your data stores · seen Aug 2026 · source · release history
- Detects API over-exposure — endpoints returning more fields than the caller is entitled to, and missing tenant ownership checks. 🚀 DSPM: Find data exposure risks without connecting your data stores · seen Aug 2026 · source · release history
- Detects over-broad third-party and AI sharing — customer data and secrets sent to vendors, analytics pipelines, LLM prompts, and vector stores. 🚀 DSPM: Find data exposure risks without connecting your data stores · seen Aug 2026 · source · release history
example
-
Point Aikido at a repository to audit sensitive data flows and exposures at the source — no database credentials needed.
In the Aikido console, go to your repository, open the 'Data Exposure Audit (DSPM)' scan, and review where sensitive data is exposed in code.#52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source -
Point DSPM at a repository to discover where sensitive data is exposed in code — no database credentials or access grants needed.
In the Aikido console, navigate to your repository, then open the Data Exposure Audit (DSPM) scan to review sensitive data flow findings and remediate at the source.#52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source
Deep Review shipped Analyses pull requests beyond the diff—examining surrounding code and linked repositories—to catch business logic mistakes and cross-service security issues.
Shared capability: Static application security testing
release 16 total
- Adds Aikido Intel vulnerability and malware intelligence into PR reviews. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history
- Enabled per repository with configurable linked repos and a review level setting; billed at 1 credit ($1) per PR with unlimited re-reviews on the same PR and a configurable monthly spend cap. 🚀Deep Review: the agentic PR review that cuts merge time and bugs shipped · seen Sep 2026 · source · release history
- Introduces Deep Review, an agentic pull request reviewer that reasons across your full codebase — including middleware, global config, and linked repositories — not just the diff.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ 🚀Deep Review: the agentic PR review that cuts merge time and bugs shipped · seen Sep 2026 · source · release history
- Saves accepted-risk and false-positive decisions to memory so future reviews reflect prior feedback. 🚀Deep Review: the agentic PR review that cuts merge time and bugs shipped · seen Sep 2026 · source · release history
- Flags bugs and unintended side effects in addition to security findings on every pull request. 🚀Deep Review: the agentic PR review that cuts merge time and bugs shipped · seen Sep 2026 · source · release history
- Runs after existing PR checks (SAST, dependency checks) to build on their findings rather than repeat them. 🚀Deep Review: the agentic PR review that cuts merge time and bugs shipped · seen Sep 2026 · source · release history
example
-
Cap monthly Deep Review spend to keep costs predictable across active repositories.
In Aikido, go to Aikido Wallet > Deep Review and set a monthly credit cap. Each PR costs 1 credit ($1) with unlimited re-reviews on the same PR.🚀Deep Review: the agentic PR review that cuts merge time and bugs shipped · seen Sep 2026 · source -
Enable Deep Review on a repository and link related repos so cross-repo logic tracing covers your full stack before merging a sensitive change.
In Aikido, navigate to your repository settings, enable Deep Review for the target repo, add linked repositories under 'Related repos', and select the review level that fits your team.🚀Deep Review: the agentic PR review that cuts merge time and bugs shipped · seen Sep 2026 · source -
Enable Deep Review on a repository and link a related repo so it reasons across both codebases when reviewing PRs.
In the Aikido console, go to your repository settings, enable Deep Review, link related repositories under 'Linked repos', and set the review level that fits your team.🚀Deep Review: the agentic PR review that cuts merge time and bugs shipped · seen Sep 2026 · source -
Keep monthly spend predictable by setting a cap on how many credits Deep Review can consume across your repos.
In the Aikido console, open Aikido Wallet settings and set a monthly credit cap to limit Deep Review spend across all enabled repositories.🚀Deep Review: the agentic PR review that cuts merge time and bugs shipped · seen Sep 2026 · source
Code Audit shipped Applies agentic reasoning to source code to uncover logic flaws—such as cross-tenant data leakage—that pattern-based scanners miss.
Shared capability: Static application security testing
release 13 total
-
Pricing shown upfront in credits before an audit starts, with cost calculated from the size and complexity of selected codebases.
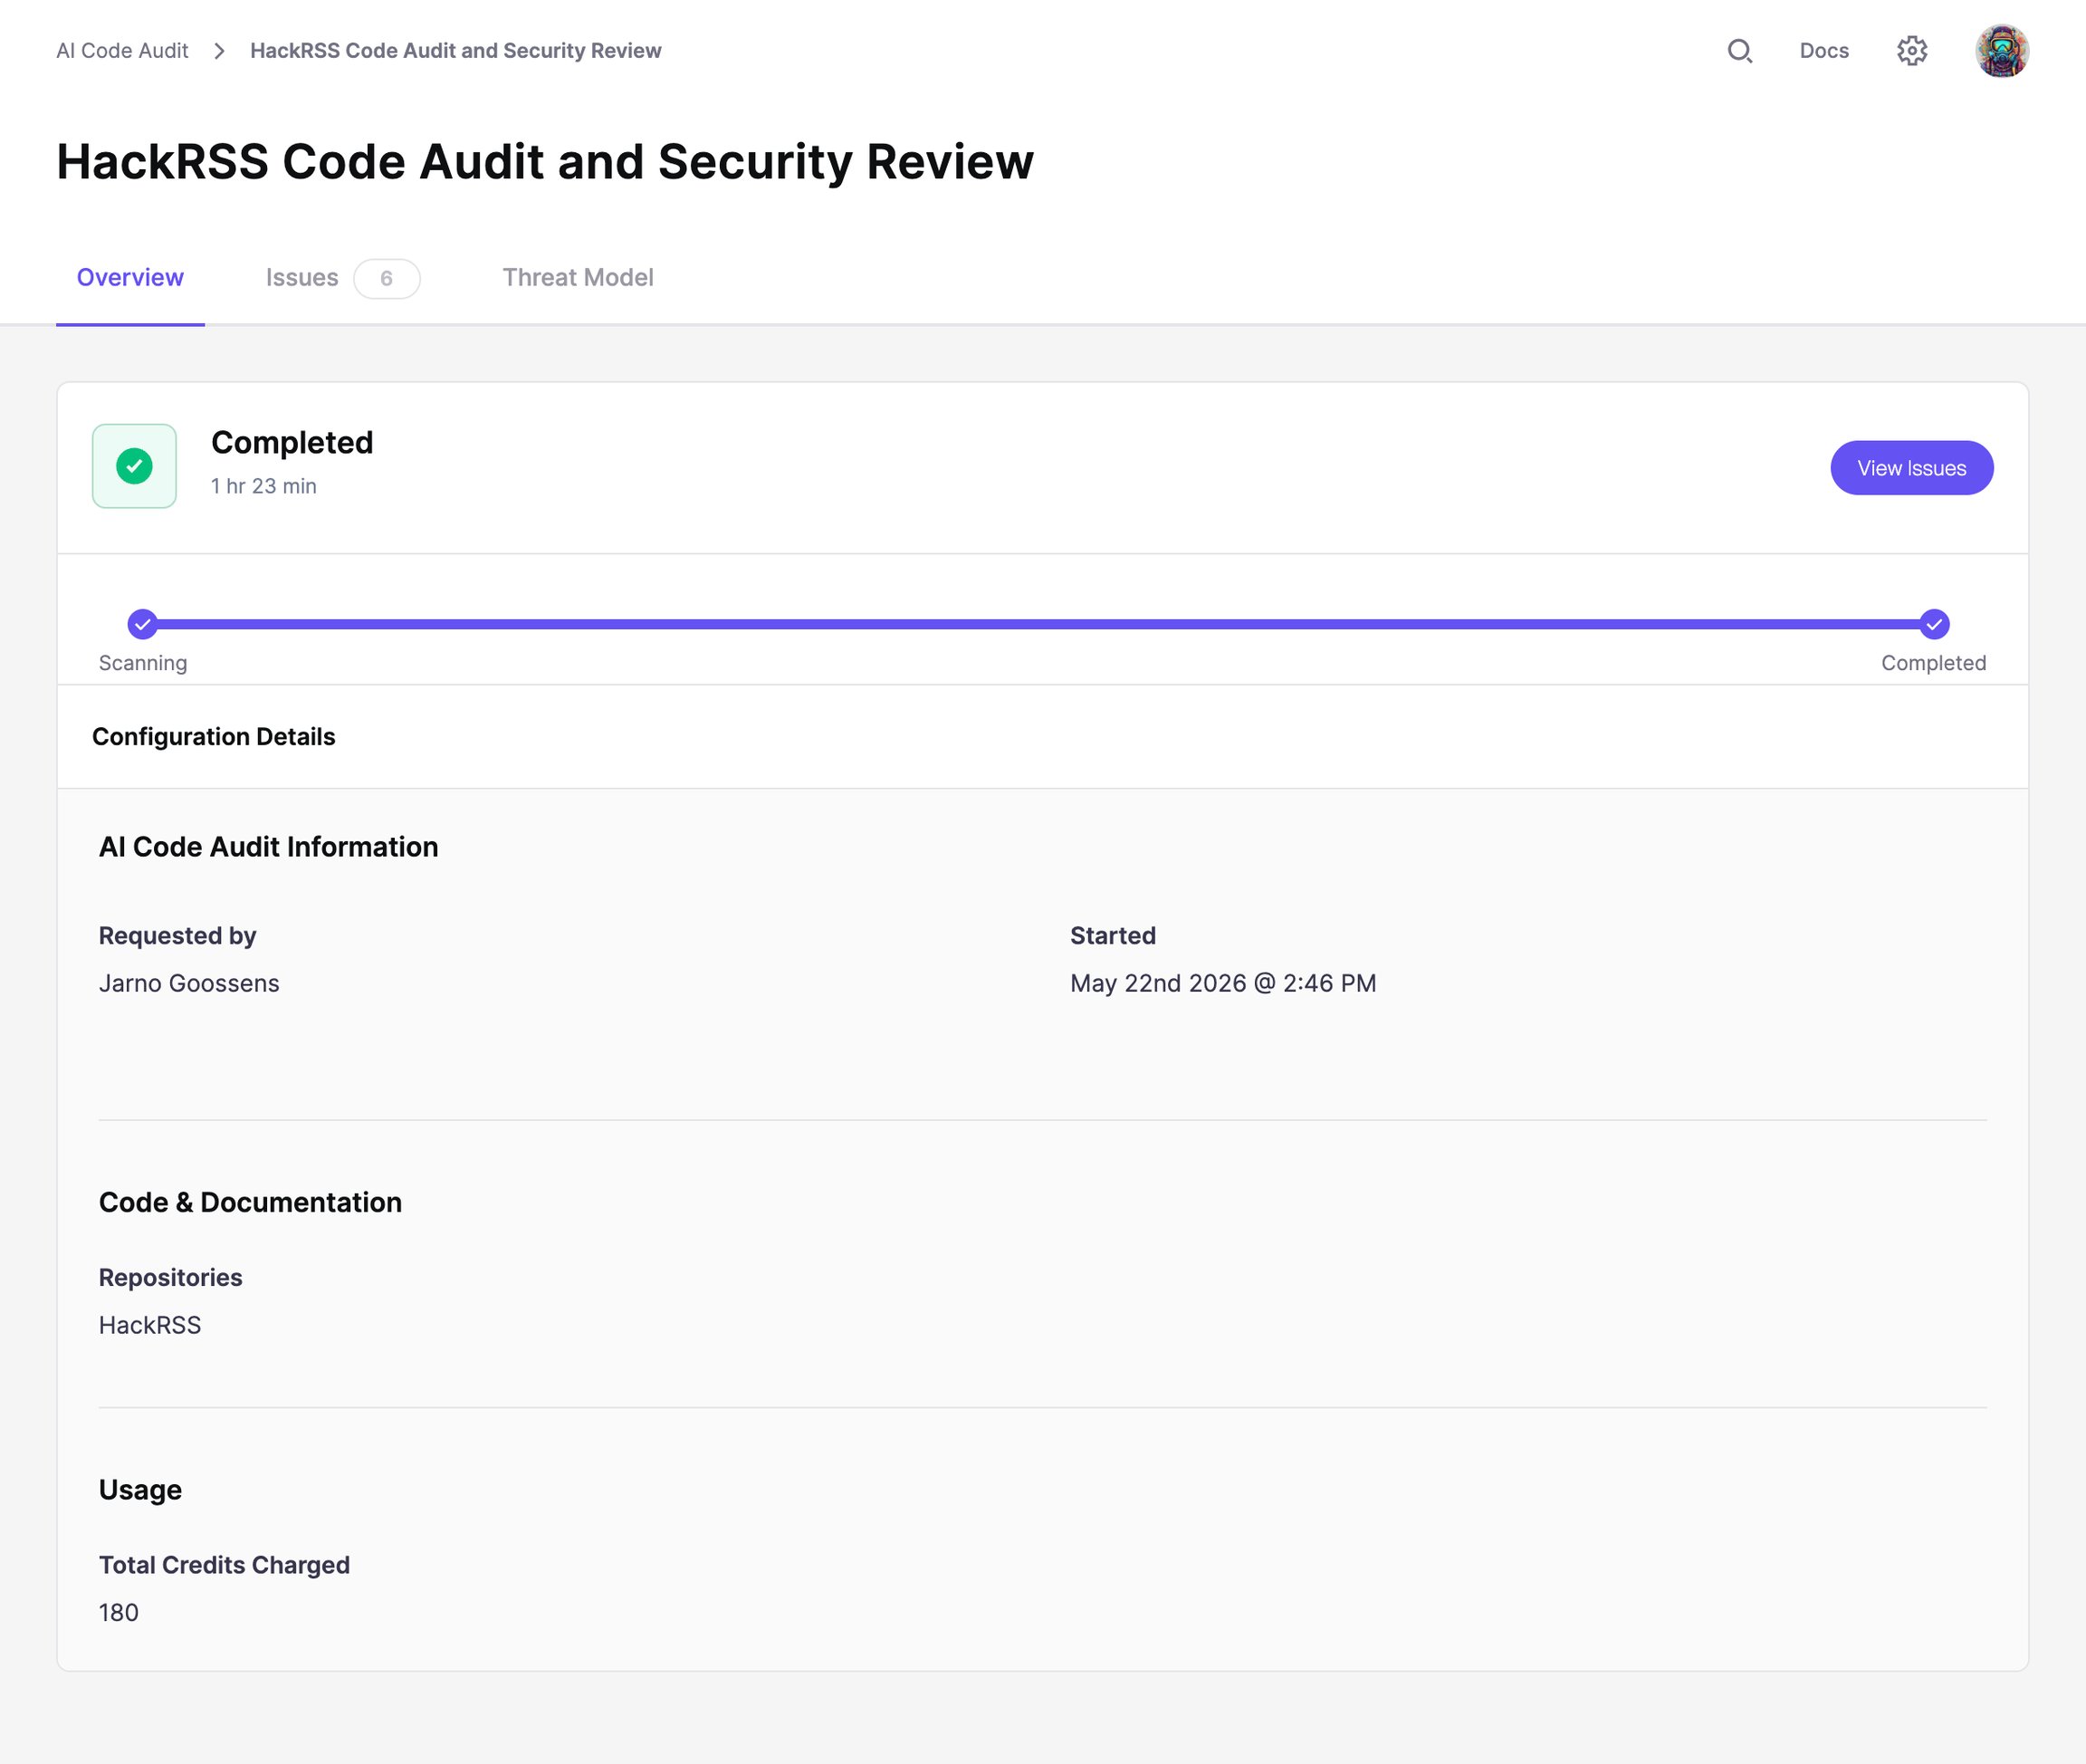 🚀Code Audit: Pentest-grade reasoning on your source code, no environment required. · seen Aug 2026
· source
· release history
-
Runs against already-connected repositories with no new data source to onboard; each audit consumes credits from the Aikido Wallet.
🚀 DSPM: Find data exposure risks without connecting your data stores · seen Aug 2026
· source
· release history
- Code Audit is priced in credits shown upfront before the audit starts, with cost based on codebase size and complexity. 🚀 Code Audit: Pentest-grade reasoning on your source code, no environment required. · seen Aug 2026 · source · release history
- New Code Audit feature runs agentic, pentest-grade security reasoning directly on source code to find logic flaws (e.g. cross-tenant data leakage) that pattern-based scanners miss — no staging URL, traffic replay, or agent deployment required. 🚀 Code Audit: Pentest-grade reasoning on your source code, no environment required. · seen Aug 2026 · source · release history
-
Each agent run is logged with a short rationale explaining what was analyzed and what actions were taken, allowing teams to review and override decisions.
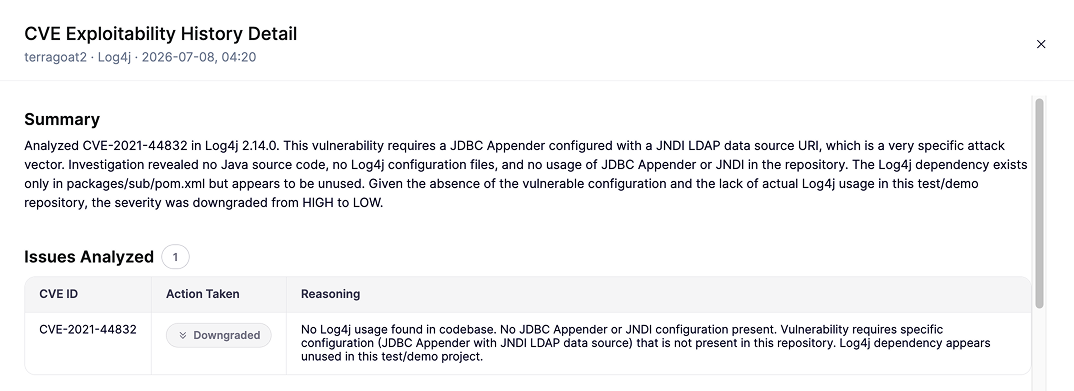 🚀 Extreme Noise Reduction for Secrets and CVEs · seen Aug 2026
· source
· release history
- Supports hard-to-test-by-URL codebases including mobile apps, smart contracts, desktop apps, embedded software, and libraries. 🚀 Code Audit: Pentest-grade reasoning on your source code, no environment required. · seen Aug 2026 · source · release history
example
-
Start a pentest-grade code audit on a repo with no live environment — useful for auditing a smart contract or mobile app codebase.
In the Aikido dashboard, go to Code Audit, connect the target repository, review the upfront credit cost, then click Start Audit.🚀Code Audit: Pentest-grade reasoning on your source code, no environment required. · seen Aug 2026 · source
SAST (Static Application Security Testing) shipped Scans source code across multiple languages to find security vulnerabilities and logic flaws, with AI-assisted analysis and custom rule context.
Shared capability: Static application security testing
Also counts toward: ML-based detection, Scripting language support
release 7 total
- Adds Azure DevOps Self-Managed Server support for source code scanning. #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · seen Jul 2026 · source · release history
- Adds Clojure support to Code Scanning. #42 - Dep Upgrade Analysis, Eclipse IDE, AI Pentest Preview & Real Time Kubernetes Image Scanning · seen Jul 2026 · source · release history
- Adds custom context on SAST rules to improve AutoTriage accuracy. #44 - Talk to Aikido Autofix, Pentest Threat Model and support for Alibaba Cloud · seen Jul 2026 · source · release history
- Sponsors Betterleaks (next Gitleaks iteration) delivering 5.2× better performance and improved accuracy. #44 - Talk to Aikido Autofix, Pentest Threat Model and support for Alibaba Cloud · seen Jul 2026 · source · release history
- Adds Visual Basic.NET support to Code Scanning. #42 - Dep Upgrade Analysis, Eclipse IDE, AI Pentest Preview & Real Time Kubernetes Image Scanning · seen Jul 2026 · source · release history
- New API endpoint to list all CI scans. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
example
-
Audit source code for logic flaws and vulnerabilities beyond what traditional SAST tools detect, using AI-powered pentest-grade analysis.
In the Aikido console, go to Code > AI Code Audit and connect a repository to trigger pentest-grade AI reasoning on your source code.#48 - AI Code Audit, Aikido MCP and ServiceNow Integration · seen Jul 2026 · source
Vulnerability prioritization 3 features Vulnerability assessment methods since 2026
AutoTriage shipped Automatically triages and prioritises security findings, using custom rule context to improve accuracy.
Shared capability: Vulnerability prioritization
release 16 total
- Saves accepted-risk and false-positive decisions to memory so future reviews learn from prior feedback on the same repository. 🚀Deep Review: the agentic PR review that cuts merge time and bugs shipped · seen Sep 2026 · source · release history
-
Adds Secrets AutoTriage: an LLM agent that runs after entropy detection to assess whether a discovered secret is a real, exposed credential, determine its liveness and scope, and automatically ignore or escalate findings based on defined rules.
🚀Extreme Noise Reduction for Secrets and CVEs · seen Aug 2026
· source
· release history
- Each AutoTriage and CVE Exploitability Analysis run is logged with a short rationale so teams can review what was analyzed and what actions the agent took. 🚀Extreme Noise Reduction for Secrets and CVEs · seen Aug 2026 · source · release history
- New Secrets AutoTriage agent runs after entropy detection to assess whether a discovered secret is a real, exposed credential — evaluating liveness, scope, and surrounding code context — then applies defined rules or LLM reasoning for ambiguous cases. 🚀 Extreme Noise Reduction for Secrets and CVEs · seen Aug 2026 · source · release history
- New API endpoint to get SLA settings. #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · seen Jul 2026 · source · release history
- New API endpoint to list snoozed and ignored issues from PRs. #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · seen Jul 2026 · source · release history
example
-
Review a Secrets AutoTriage outcome to confirm or override the agent's liveness and scope assessment for an ambiguous credential.
In the Aikido console, open a secrets finding > AutoTriage result to read the agent's explanation of the credential type, liveness, and risk level, then accept or override the decision.New - Extreme Noise Reduction for Secrets and CVEs 🚀 · seen Jul 2026 · source
Issue reachability analysis shipped Determines whether a vulnerability is reachable in the deployed environment and shows that context alongside the finding.
Shared capability: Vulnerability prioritization
Also counts toward: REST API
release 9 total
-
Agents chain multi-step findings (for example: exposed
.gitfolder → SSH credentials → Azure admin access) and include the full exploit chain in the report so teams can see what an attacker could actually reach.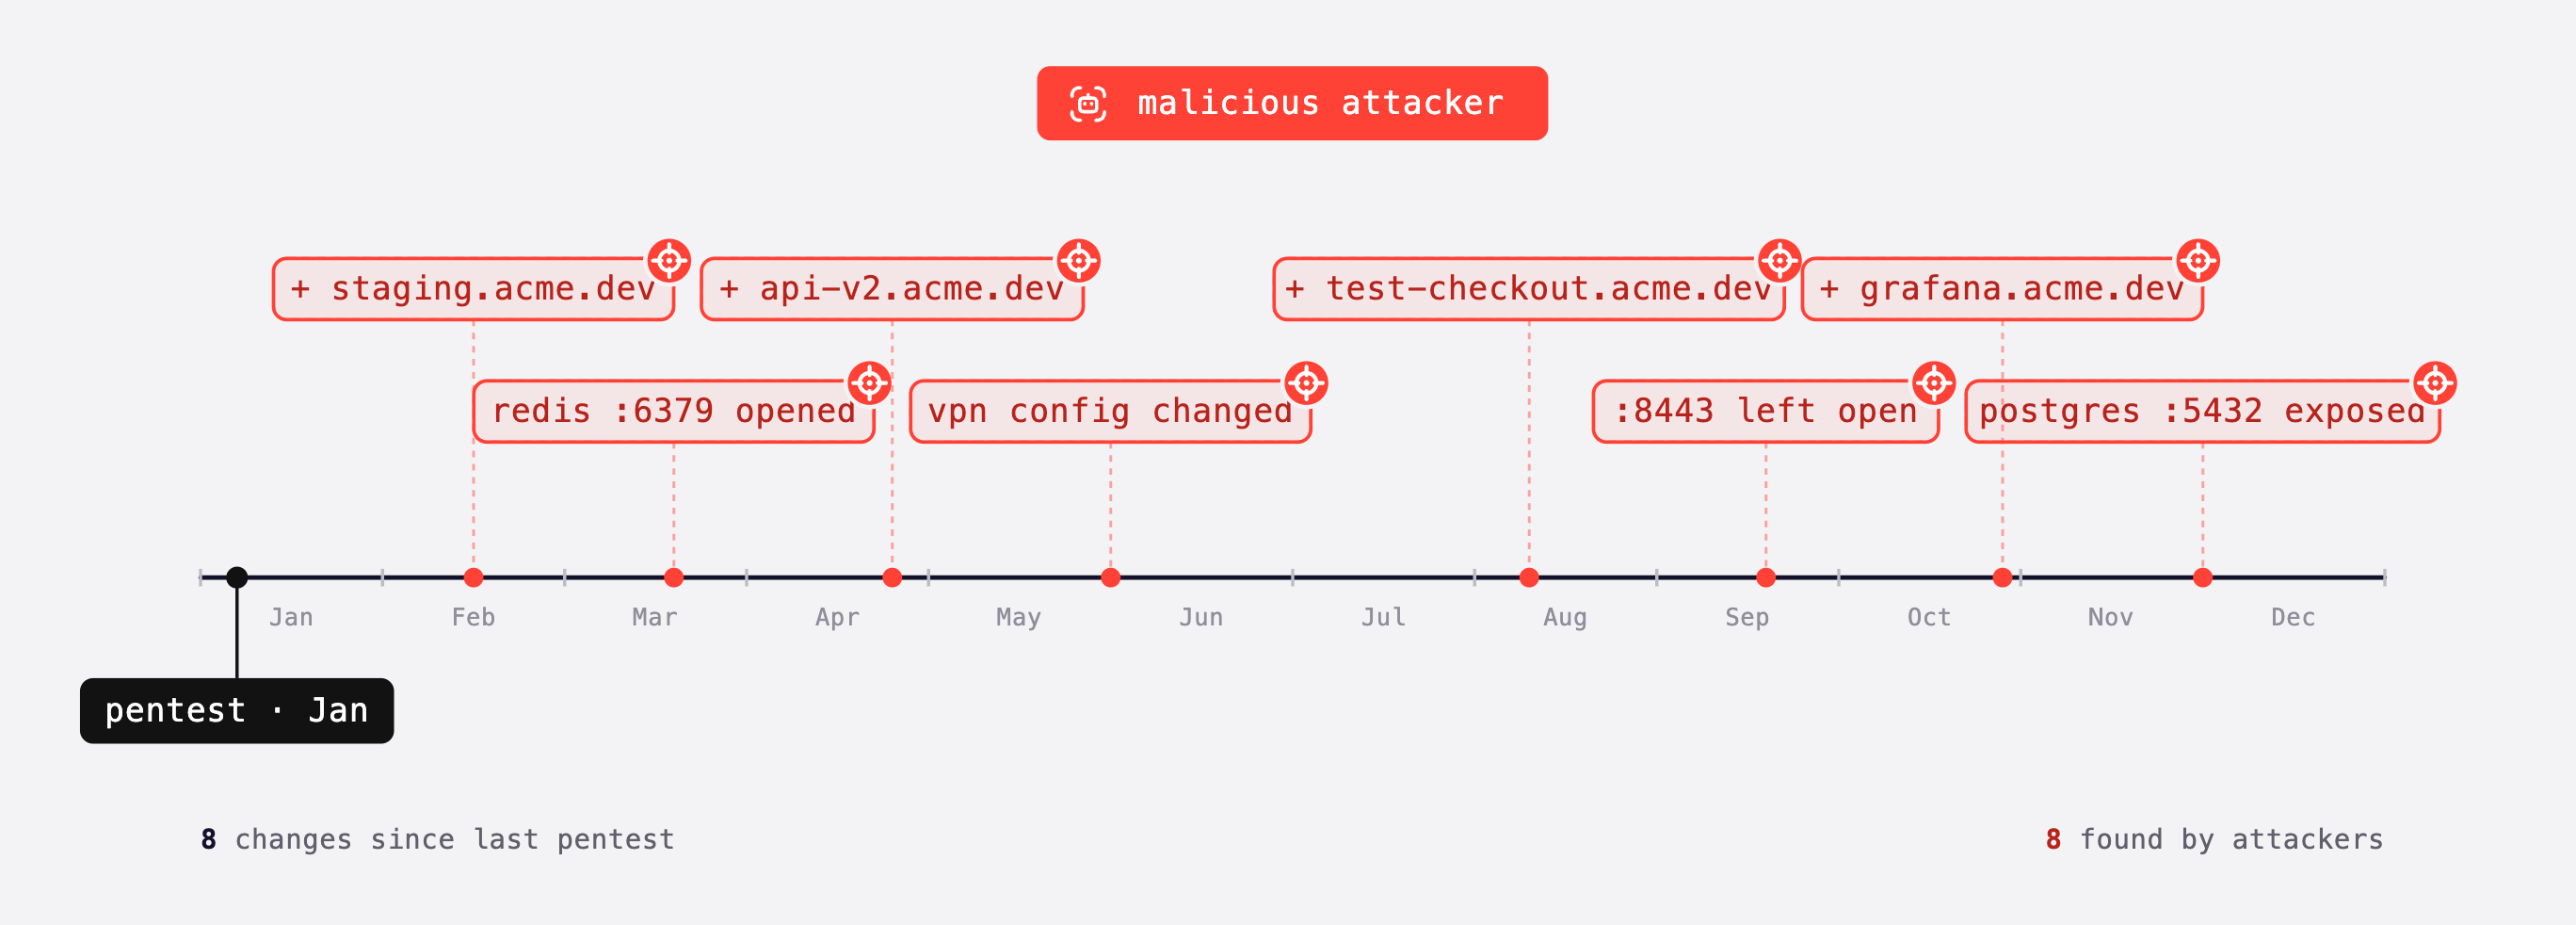 announced · Oct 2026
· source
· release history
- Extends Container scanning Reachability to include BigQuery datasets. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
- Makes VM Reachability available for GCP in Cloud scanning. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
-
New CVE Exploitability Analysis agent evaluates whether a CVE is actually reachable and exploitable in your codebase using LLM reasoning over how your code uses the affected package.
🚀 Extreme Noise Reduction for Secrets and CVEs · seen Aug 2026
· source
· release history
- New API endpoint to get issue reachability analysis. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
- New CVE Exploitability Analysis agent: uses LLM reasoning against your actual codebase to determine whether a CVE is reachable and how urgently it must be addressed. New - Extreme Noise Reduction for Secrets and CVEs 🚀 · seen Jul 2026 · source · release history
Cloud reachability analysis shipped Maps complete network paths to cloud resources to determine whether a finding is reachable from the internet.
Shared capability: Vulnerability prioritization
release 7 total
- Extends cloud reachability analysis for containers to Google Cloud Run. #46 - Escalating your AI Pentest and Additional Context for AutoTriage · seen Jul 2026 · source · release history
- New Reachability Diagrams for Cloud VMs: visualizes whether a finding is exploitable by mapping the network path, entry points, and exposed ports in your cloud environment. #43 - Aikido Infinite (Continuous Pentesting), VM Reachability Diagrams & IDE full scan · seen Jul 2026 · source · release history
- Displays CVEs on VM attack path diagrams in Cloud & VM views. #44 - Talk to Aikido Autofix, Pentest Threat Model and support for Alibaba Cloud · seen Jul 2026 · source · release history
- Extends Virtual Machine Reachability support to Azure. #45 - Aikido × Lovable - Vibe, Fix, Ship and Container Reachability · seen Jul 2026 · source · release history
- Adds Container Reachability: maps the complete network route to running containers and surfaces CVEs in deployment context, showing what is exposed to the internet. #45 - Aikido × Lovable - Vibe, Fix, Ship and Container Reachability · seen Jul 2026 · source · release history
- Continuous Pentest adds Azure support for cloud environment scanning. #50 - Agentic Dependency AutoFix, Registry Proxy and Device Protection adds Ruby and Rust · seen Jul 2026 · source · release history
example
-
Visualize the network path to a vulnerable cloud VM to quickly assess real-world exploitability before prioritizing remediation.
In the Aikido console, open a Cloud VM finding, then select 'Reachability Diagram' to view the network path, entry points, and exposed ports leading to the affected resource.#43 - Aikido Infinite (Continuous Pentesting), VM Reachability Diagrams & IDE full scan · seen Jul 2026 · source
Web vulnerability scanning 2 features Vulnerability assessment methods since 2026
AI Pentest agent shipped Automatically penetration-tests applications and re-tests them after every code change to validate whether findings are genuinely exploitable.
Shared capability: Web vulnerability scanning
Also counts toward: Multi-factor authentication, Scheduled jobs
release 34 total
- Introduces Aikido Altar, the first open-weight security model, powering air-gapped, on-prem pentesting via Aikido Machine so code never leaves the infrastructure. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history
- Launches Altar, Aikido's first open-weight security model built to run frontier-grade pentesting fully on-prem and air-gapped without sending data to third parties. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
- Adds Pentest for AI Capabilities targeting the OWASP Agentic Top 10 (including prompt injection and memory poisoning) for agents and LLM features. #55 - Code Coverage for Github, SIEM Integrations and Pentest for AI capabilities · seen Sep 2026 · source · release history
- Adds targeted pentest for AI capabilities covering OWASP Agentic Top 10 #55 - Code Coverage for Github, SIEM Integrations and Pentest for AI capabilities · Sep 2026 · source · release history
-
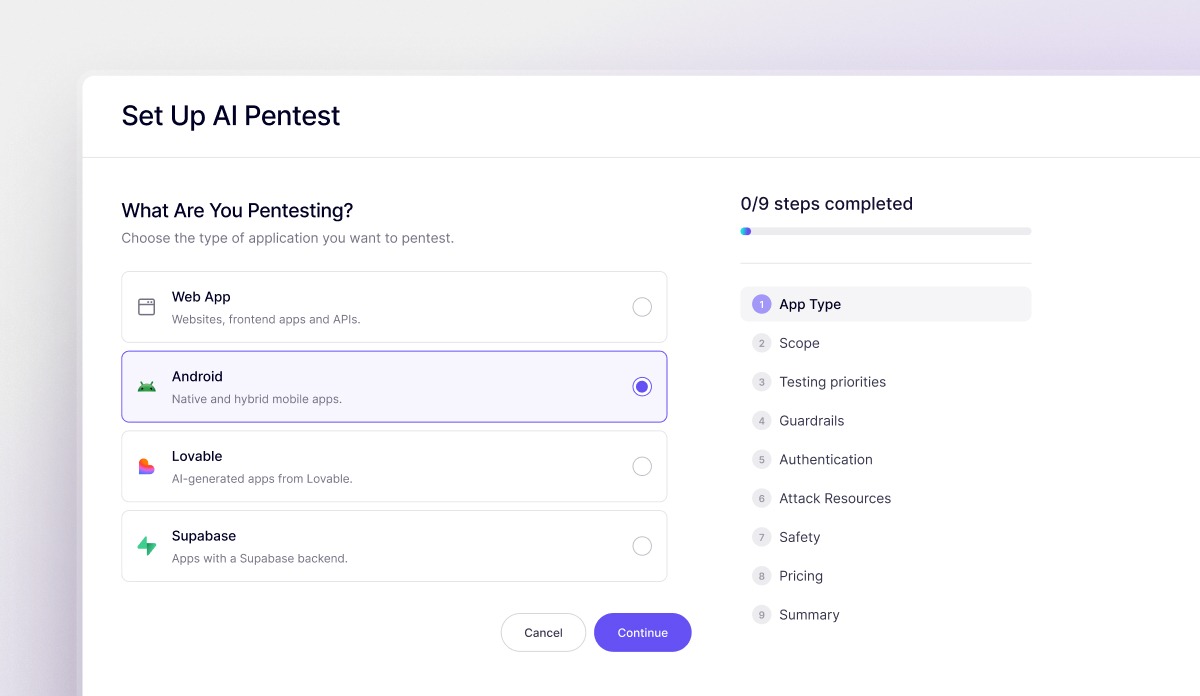
Supports simultaneous assessment of the Android app and its backend API in a single run — API findings appear in the same report as app findings.
 announced · Aug 2026
· source
· release history
- Android pentests are rightsized — Aikido's indexer scales the assessment scope to the actual app size rather than charging a flat fee. announced · Aug 2026 · source · release history
example
-
Launch a code audit on a connected repo directly from the Aikido console — no staging URL or pentest scope needed.
In the Aikido console, go to Code Audit, select the target codebase, review the credit cost shown upfront, and click Start Audit.New - Code Audit: Pentest-grade reasoning on your source code, no environment required. 🚀 · seen Jul 2026 · source -
Trigger a targeted re-test of a single AI Pentest finding after applying a fix, instead of re-running the full pentest.
In the Aikido console, navigate to AI Pentest > Findings, select the individual finding you fixed, and click 'Re-test' to have Aikido verify the fix in isolation.#41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source
External Network Pentest shipped Scans internet-exposed assets—including forgotten subdomains and open admin panels—and confirms findings with evidence.
Shared capability: Web vulnerability scanning
release 12 total
- External network pentests produce an auditor-ready report in the same format as Aikido's web app and mobile pentests, covering the attack surface up to the login page. 🚀External Network Pentesting: test your perimeter before someone else does · seen Oct 2026 · source · release history
- A scoping agent checks how much of each subdomain you own and limits testing to the parts you control, with all agent traffic routed through a proxy that blocks out-of-scope connections. 🚀External Network Pentesting: test your perimeter before someone else does · seen Oct 2026 · source · release history
- Agents chain findings across hosts — using credentials or access found on one system to pivot to the next — and the report shows the full attack path from entry point to impact. 🚀External Network Pentesting: test your perimeter before someone else does · seen Oct 2026 · source · release history
- Aikido Security now offers an External Network Pentesting capability where AI agents discover subdomains, open ports, and services from a list of top-level domains, then attempt exploitation using known CVEs, misconfigurations, and exposed secrets.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ 🚀External Network Pentesting: test your perimeter before someone else does · seen Oct 2026 · source · release history
- Control test intensity by setting a maximum requests per second per target, or restrict testing to inside or outside business hours. 🚀External Network Pentesting: test your perimeter before someone else does · seen Oct 2026 · source · release history
- Watch agents work in real time via the Agents tab, which shows each agent's current thinking, tools in use, and findings so far. 🚀External Network Pentesting: test your perimeter before someone else does · seen Oct 2026 · source · release history
example
-
Enable continuous mode so newly exposed subdomains are automatically tested shortly after they go live, without manually kicking off a new pentest.
1. In the Aikido console, open your External Network Pentest configuration. 2. Under 'Run mode', select 'Continuous'. 3.🚀External Network Pentesting: test your perimeter before someone else does · seen Oct 2026 · source -
Start an external network pentest against your perimeter by supplying your top-level domains through the Aikido console.
1. In the Aikido console, navigate to Pentesting > External Network Pentesting. 2. Add one or more top-level domains to scope. 3.🚀External Network Pentesting: test your perimeter before someone else does · seen Oct 2026 · source -
Start an external network pentest when you want to see everything attackers can reach under your domain before they do.
In the Aikido product, go to Pentesting > External Network, enter your root domain, verify ownership, review the auto-generated asset list (remove any hosts you do not want tested), confirm the…announced · Oct 2026 · source
Container image vulnerability scanning 1 feature Vulnerability assessment methods since 2026
Container image scanning shipped Scans container images for vulnerabilities with flexible include/exclude filtering.
Shared capability: Container image vulnerability scanning
Also counts toward: REST API
release 16 total
-
Adds Terraform Container management resources and publishes the Aikido provider to the OpenTofu registry.
 #58 - Cloud Security Audits, External Network Pentesting and Aikido is now FedRAMP Moderate · seen Oct 2026
· source
· release history
- New API to request a hardened container image. #54 - Device Protection for Linux and VM Scanning for Google Cloud · seen Aug 2026 · source · release history
- Kubernetes team annotations are now surfaced as container labels in Cloud. #53 - Deep Review, Android Pentests, Custom Reports and Free Credits · seen Aug 2026 · source · release history
- Noise reduction for container images in cloud scanning reduces alert fatigue. #52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source · release history
- Noise reduction for container images in Cloud scans. #52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source · release history
- Kubernetes registry option added for public image scanning. #52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source · release history
Infrastructure-as-code security scanning 1 feature Vulnerability assessment methods
Cloud Security Audit shipped Uses AI agents to reason across cloud and IaC configurations to surface multi-step attack paths, linking each finding back to the causative template.
Shared capability: Infrastructure-as-code security scanning
release
-
New Cloud Security Audit feature: AI agents reason across cloud and IaC configurations to surface multi-step attack paths and link each finding back to the causative template.
#58 - Cloud Security Audits, External Network Pentesting and Aikido is now FedRAMP Moderate · seen Oct 2026
· source
· release history
SAML SSO 1 feature Identity and access since 2026
SCM platform integrations shipped Integrates with GitHub and GitLab to support PR-level actions such as ignoring findings, importing labels, and linking users to teams.
previously: GitHub integration, GitHub and GitLab integration
Shared capability: SAML SSO
release 15 total
- Introduces a Terraform provider to manage repositories, AutoFix, PR checks, teams, and permissions as code for large-scale rollouts without UI interaction. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history
-
Adds
GET /api/pr-check-detailendpoint to retrieve PR check details programmatically.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history - Integrates natively with GitHub, GitLab, Bitbucket, and Azure DevOps SCM platforms, with a custom integration path for other platforms. 🚀Code Coverage: find what your tests miss · seen Sep 2026 · source · release history
-
Adds
API - Manage defaults PR checks for new reposendpoint to control default PR check configuration via the API. #55 - Code Coverage for Github, SIEM Integrations and Pentest for AI capabilities · seen Sep 2026 · source · release history -
Adds
new resource to manage default PR checksandnew resource to manage PR check settingsto the Aikido Terraform provider. #55 - Code Coverage for Github, SIEM Integrations and Pentest for AI capabilities · seen Sep 2026 · source · release history - New API to bulk update GitHub PR configuration across repositories. #54 - Device Protection for Linux and VM Scanning for Google Cloud · seen Aug 2026 · source · release history
Outbound webhooks (the product notifies you) 1 feature Interfaces and integrations since 2026
Webhooks shipped Emits webhook events for security finding lifecycle changes, such as manual severity updates, to support custom automation.
Shared capability: Outbound webhooks (the product notifies you)
Also counts toward: REST API, Outbound webhooks (the product notifies you)
release 7 total
- Adds webhook event for when a new issue ignore/snooze request is accepted or denied. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
-
Adds API endpoints for user login history (
list user logins history), broker management, and webhook triggers for issue ignore/snooze decisions and domain scan completion. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · Sep 2026 · source · release history - New API webhook for manual severity changes. #44 - Talk to Aikido Autofix, Pentest Threat Model and support for Alibaba Cloud · seen Jul 2026 · source · release history
- New API endpoints to manage webhooks, manage excluded paths per repository, and set custom headers for webhooks. #45 - Aikido × Lovable - Vibe, Fix, Ship and Container Reachability · seen Jul 2026 · source · release history
- Adds API endpoint to Get SLA settings #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · Jul 2026 · source · release history
- Adds API endpoints to manage webhooks for repositories. #45 - Aikido × Lovable - Vibe, Fix, Ship and Container Reachability · Apr 2026 · source · release history
Other / not yet classified 35 features Features we have not matched to a capability yet. A suggested match is marked.
Developer device inventory and protection shipped Maintains a live inventory of packages and extensions on developer devices, blocks malware on install, and contributes device-level data to the SBOM.
Also counts toward: Scripting language support
release 29 total
- Adds archived device status to Device Protection. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history
-
Adds
DELETE /api/device(Remove a device from device protection) endpoint. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history - Adds Firefox and Homebrew as new ecosystems in Device Protection. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
- Adds a new Firewall to Device Protection to block malicious domains. #55 - Code Coverage for Github, SIEM Integrations and Pentest for AI capabilities · seen Sep 2026 · source · release history
-
Adds
API - Listing & handling inbox requestsendpoint to manage inbox requests via the API. #55 - Code Coverage for Github, SIEM Integrations and Pentest for AI capabilities · seen Sep 2026 · source · release history -
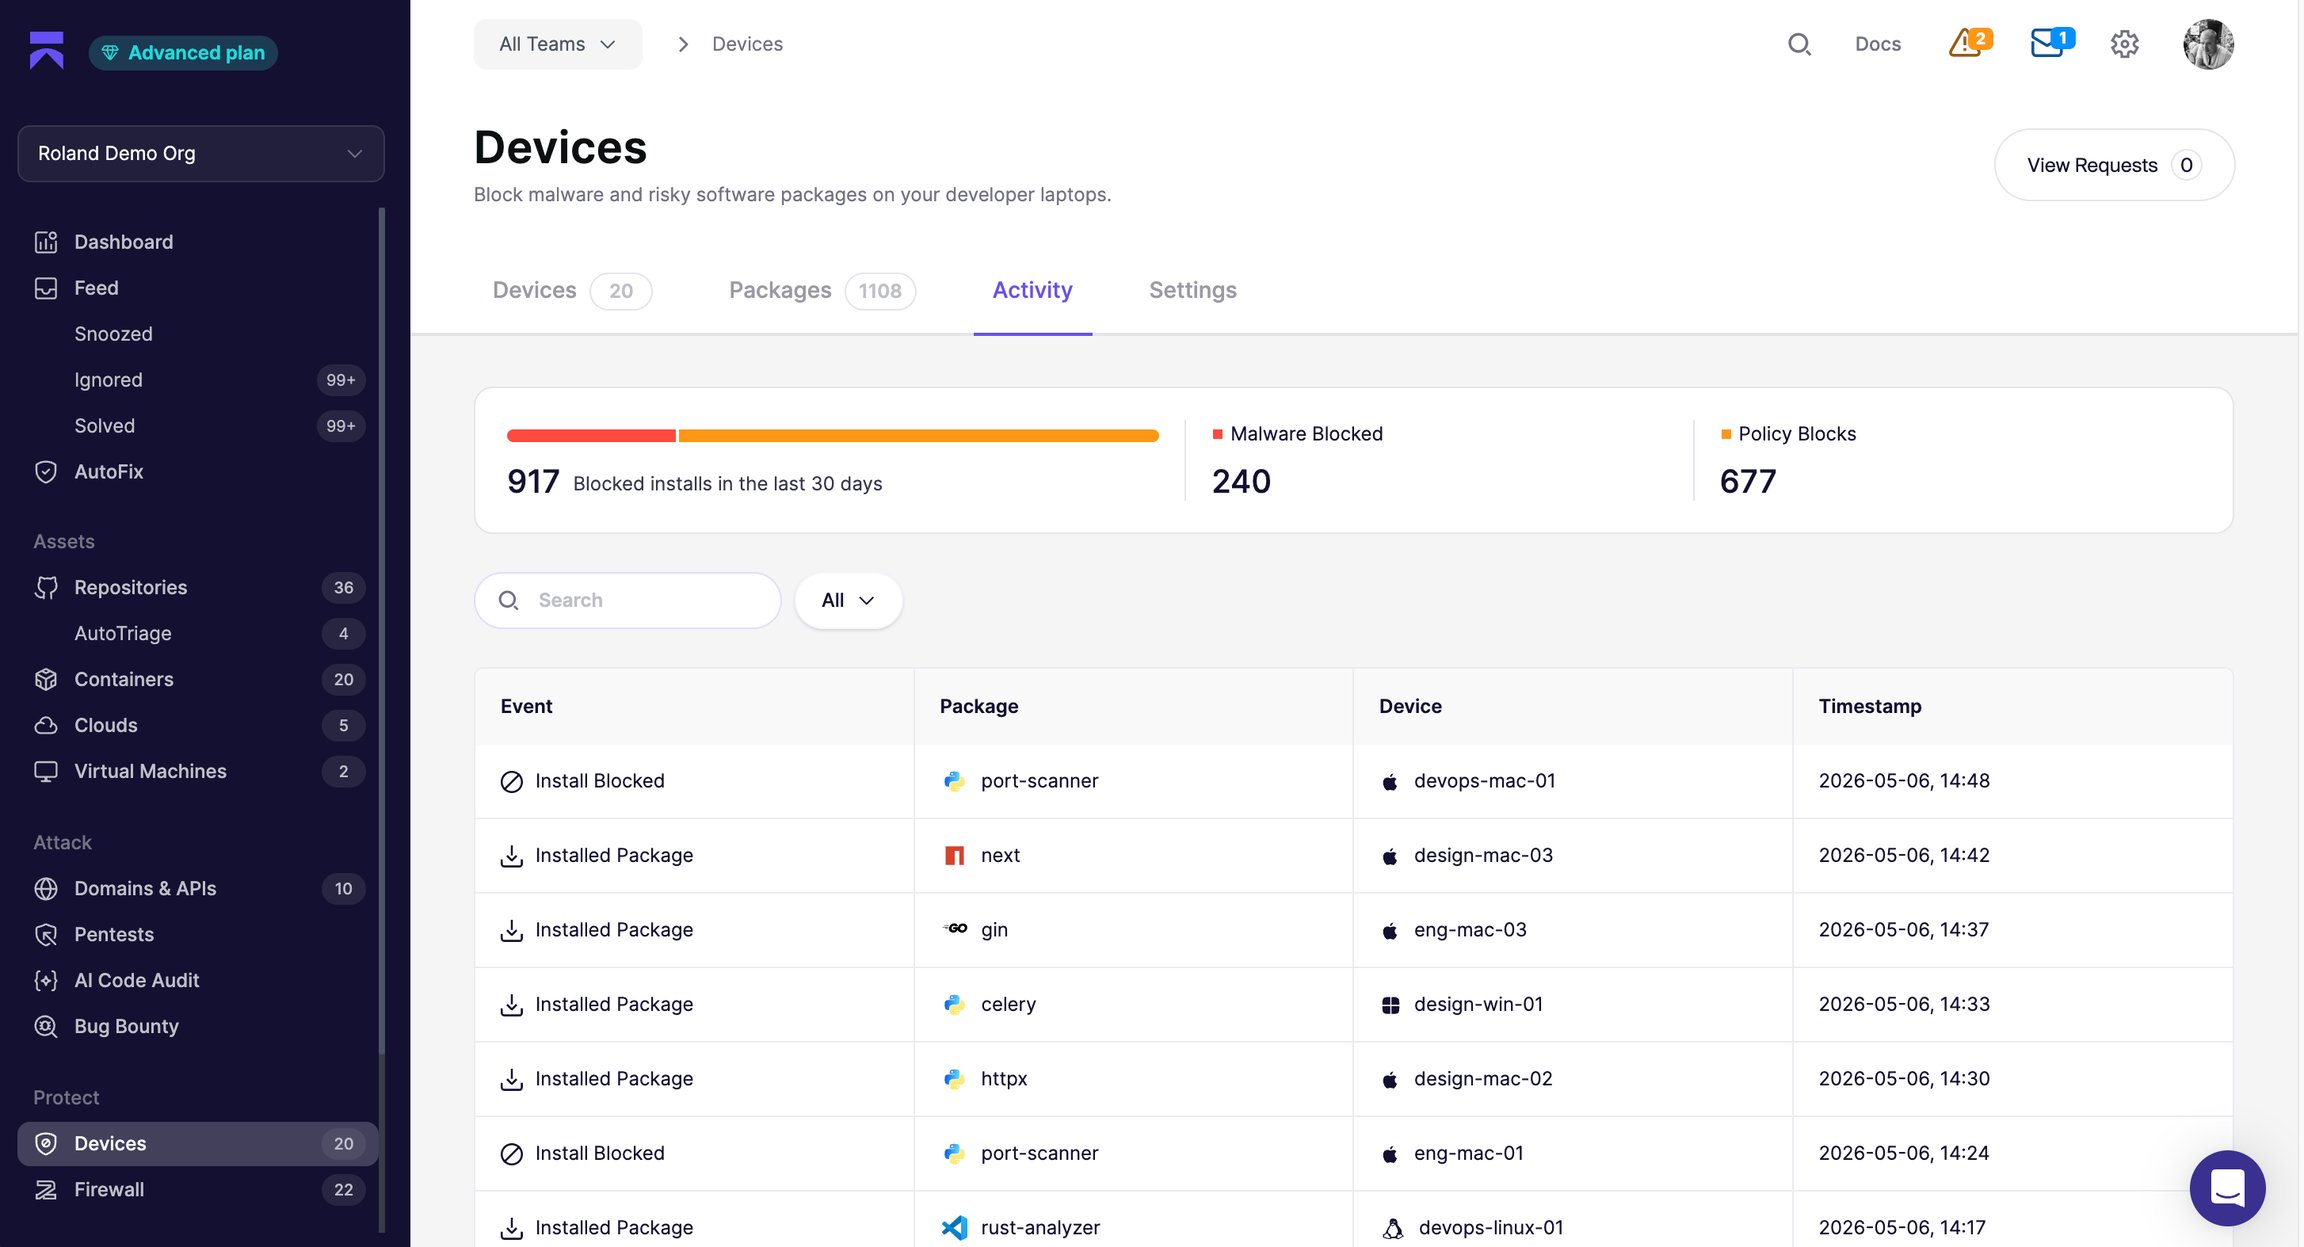
Request-and-approval workflow pauses blocked installs and routes a one-click exception request to the admin Inbox inside Aikido.
 🚀Protect Company Devices From Supply Chain Attacks · seen Aug 2026
· source
· release history
example
-
Review and act on a developer's blocked-install exception request from the admin Inbox.
In the Aikido console, go to Inbox, find the pending install request, review the flagged package name and policy reason, then approve or deny the exception.🚀Protect Company Devices From Supply Chain Attacks · seen Aug 2026 · source -
Export an SBOM for a specific device to inventory software components and feed downstream vulnerability management tools.
In the Aikido console, go to Endpoint > Devices > select a device > Export SBOM.#49 - Visualize Threat models, Device Protection for Windows and Labels on Repositories & Containers · seen Jul 2026 · source
Zen Firewall (runtime protection) shipped Deploys in-app firewall agents across multiple language runtimes to block attacks at runtime.
Also counts toward: Agent-based deployment, Python scripting support, Scripting language support
release 28 total
-
Adds Zen Firewall agent releases for Dotnet, Python,
PHP, Ruby, and Node.
#58 - Cloud Security Audits, External Network Pentesting and Aikido is now FedRAMP Moderate · seen Oct 2026
· source
· release history
-
Adds
GET /api/zen-user-ips(List Zen user IPs) endpoint. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history - Expands Zen Firewall agent support to Dotnet, Python, PHP, Golang, and Node. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history
- Adds Alpine support for the Zen Firewall PHP agent. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
- Adds Zen Firewall agent releases for Java, PHP, Golang, and Node. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
- Releases Zen Firewall agents for Java, PHP, Golang, Node, and Alpine Linux. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · Sep 2026 · source · release history
AutoFix shipped Automatically generates code fixes for security findings and lets developers refine them in plain language to match team conventions.
Also counts toward: Built-in AI assistant
release 21 total
-
Adds
GET /PUT /api/container-autofix-settings(Get or update container AutoFix settings) endpoint. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history -
Code Audit surfaces code-based evidence, root cause analysis, and remediation guidance, plus AI-powered AutoFix for creating remediation PRs in a few clicks.
🚀Code Audit: Pentest-grade reasoning on your source code, no environment required. · seen Aug 2026
· source
· release history
- AutoFix generates remediation PRs from Code Audit findings with a few clicks, alongside root cause analysis and remediation guidance. 🚀 Code Audit: Pentest-grade reasoning on your source code, no environment required. · seen Aug 2026 · source · release history
- New API surface to read and update AutoFix settings. #53 - Deep Review, Android Pentests, Custom Reports and Free Credits · seen Aug 2026 · source · release history
-
Provides
AutoFixto automatically open a PR with code-level remediation for identified data exposure findings.
🚀 DSPM: Find data exposure risks without connecting your data stores · Aug 2026
· source
· release history
- New Aikido Libraries capability delivers PRs that backport open-source CVE fixes to the exact version already running, avoiding major-version bumps or breaking changes. #52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source · release history
example
-
After merging an AutoFix PR for a confirmed Android finding, retest against the patched build without rescoping.
In the Aikido console, open the original Android assessment, go to the overview tab, upload the rebuilt APK, then click 'Retest' on any finding from the initial pentest.
announced · Aug 2026
· source
-
Merge a backported CVE fix for an existing dependency version without upgrading to a new major version.
In the Aikido console, go to Aikido Libraries, select an open-source CVE affecting your current dependency version, and open the generated PR to apply the backported patch.#52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source -
Iteratively refine an AutoFix to match your team's code conventions using natural language inside Aikido.
In the Aikido UI, open an AutoFix suggestion, click 'Refine with Aikido AI', and type a natural-language instruction such as 'Use async/await instead of callbacks and follow our error-handling…#44 - Talk to Aikido Autofix, Pentest Threat Model and support for Alibaba Cloud · seen Jul 2026 · source -
Use the AI Chat inside the AutoFix modal to refine a generated fix without leaving the product — useful when the suggested PR needs a small scope adjustment.
In the console, open a finding in the Code Analysis or AutoFix modal, then use the embedded Aikido AI Chat panel to describe the change you want (e.g., 'Scope the fix to only the affected function,…#47 - Aikido Device Protection and Aikido AI Chat · seen Jul 2026 · source -
Add organization-specific context (custom libraries, internal policies) so AutoFix generates more accurate PRs tailored to your codebase.
# Place a .aikido file at the root of your repository with custom context echo 'We use our internal wrapper `safe_query()` instead of raw DB calls.' > .aikido#47 - Aikido Device Protection and Aikido AI Chat · seen Jul 2026 · source
Code Coverage shipped Tracks per-repository, per-file, and per-line test coverage by ingesting LCOV and Cobertura reports from CI, merging multi-service reports into a unified view, displaying trends over time, and optionally blocking PRs that drop below a configured coverage threshold.
Also counts toward: CI/CD pipeline integration
release 22 total
- Provides a Code Tree tab (directory structure view) and a File List tab (files ranked by coverage percentage) for browsing coverage results. 🚀Code Coverage: find what your tests miss · seen Oct 2026 · source · release history
- Enables PR gating on GitHub: pull requests that drop coverage below a configured threshold are blocked from merging. 🚀Code Coverage: find what your tests miss · seen Oct 2026 · source · release history
- Extends code-coverage support to GitLab, BitBucket, Azure DevOps, and custom integrations. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history
-
Accepts
LCOVand Cobertura coverage report formats, with native output from Jest and pytest-cov. 🚀Code Coverage: find what your tests miss · seen Oct 2026 · source · release history -
Adds
Code Quality > Code Coveragesection showing per-repository, per-file, and per-line test coverage alongside existing code quality findings.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ 🚀Code Coverage: find what your tests miss · seen Oct 2026 · source · release history - Tracks coverage over time with a trend graph updated on each upload, visible per repository. 🚀Code Coverage: find what your tests miss · seen Oct 2026 · source · release history
example
-
Gate a GitHub PR from merging when test coverage drops, by setting up the Aikido coverage upload step after your test suite in CI.
In Aikido, go to Code Quality > Code Coverage, select your repository, and follow the setup guide to add the GitHub Action upload step after your test step, pointing it at your LCOV or Cobertura…🚀Code Coverage: find what your tests miss · seen Oct 2026 · source -
Navigate to the per-file line coverage view in Aikido to check what tests already cover before editing a flagged file.
1. In Aikido, go to Code Quality > Code Coverage. 2. Select the repository from the repo list. 3. Open the 'File List' tab to sort files by coverage percentage. 4.🚀Code Coverage: find what your tests miss · seen Sep 2026 · source
IDE plugins shipped suggested Provides IDE extensions for VSCode, JetBrains, Visual Studio, and Eclipse that surface secrets, vulnerabilities, and IaC issues as developers code.
Suggested capability: Static application security testing. This is our guess, not confirmed.
release 23 total
- Adds multi-project scanning support to the JetBrains IDE plugin. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history
- Switches VSCode secrets scanning to use BetterLeaks. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history
- Adds new JetBrains IDE plugin release with support for multi-repository scanning. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
- New VSCode IDE extension release. #54 - Device Protection for Linux and VM Scanning for Google Cloud · seen Aug 2026 · source · release history
- Adds new IDE extensions for VSCode and Visual Studio. #53 - Deep Review, Android Pentests, Custom Reports and Free Credits · seen Aug 2026 · source · release history
- IDE extensions updated with new releases for VSCode, JetBrains, and Visual Studio. #52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source · release history
Cloud misconfiguration scanning shipped Scans cloud environments across multiple providers for misconfigurations, exposed resources, and risky settings.
release 19 total
- Adds new infrastructure-focused checks to cloud scanning. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
-
Detects over-permissioned IAM roles and OAuth scopes, and unauthenticated data stores.
🚀 DSPM: Find data exposure risks without connecting your data stores · seen Aug 2026
· source
· release history
- Bulk assignment of cloud accounts to teams now available in Settings. #52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source · release history
- Bulk assignment of cloud accounts to teams available in Settings. #52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source · release history
- Adds Render cloud misconfiguration scanning. #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · seen Jul 2026 · source · release history
- Adds Terraform module for GCP project/organization onboarding. #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · seen Jul 2026 · source · release history
example
-
Assign multiple cloud accounts to a team in bulk rather than one at a time.
In the Aikido console, go to Settings > Clouds, select the cloud accounts you want to assign, and use 'Bulk assignment' to map them to a team.#52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source
Code Quality scanning shipped Scans source code for quality issues, automatically filtering out generated files to reduce noise.
Also counts toward: User-defined detection rules
release 12 total
-
Removes the maximum-rule restriction for Code Quality scans and enables auto-creation of PRs for issues found in full repository scans.
#58 - Cloud Security Audits, External Network Pentesting and Aikido is now FedRAMP Moderate · seen Oct 2026
· source
· release history
- Supports creating Task Tracker issues for Code Quality findings. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
- New Code Quality Repository Scans surface existing code quality issues across repos to help find and prioritize technical debt over time. #52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source · release history
- New Code Quality rule: Keep the diff minimal. #52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source · release history
- Code Quality PR/MR Gating by Severity enables blocking merges based on issue severity. #52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source · release history
- PR/MR gating by severity now available on GitHub for Code Quality findings. #52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source · release history
example
-
Gate pull requests on code quality severity so high-severity issues block merges automatically.
In the Aikido console, go to Code Quality settings for your repository and enable 'PR/MR Gating by Severity', then select the minimum severity threshold to block.#52 - DSPM, Aikido Libraries and Repository Code Quality scans · seen Jul 2026 · source -
Trigger a full repository code quality scan to find hotspots across the entire codebase, not just open PRs.
In the Aikido console, go to Code Quality > Repository Scan (early access) and initiate a full codebase scan to view quality trends and refactoring hotspots.#51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · seen Jul 2026 · source
Task tracker integrations shipped Automatically converts security findings into tickets in connected task trackers such as ServiceNow, with support for multiple trackers at once.
Also counts toward: Ticketing integration
release 12 total
-
Adds
POST /api/teams-to-projects(Map teams to projects) endpoint. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history - Adds auto-close for resolved code quality tickets. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history
- Adds ticket integration support for GitHub Server and Azure DevOps Cloud. #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · seen Jul 2026 · source · release history
- Task Trackers now support configuration of multiple task trackers simultaneously. #49 - Visualize Threat models, Device Protection for Windows and Labels on Repositories & Containers · seen Jul 2026 · source · release history
- New ServiceNow integration automatically converts security findings into ServiceNow tickets, routing them into existing team workflows. #48 - AI Code Audit, Aikido MCP and ServiceNow Integration · seen Jul 2026 · source · release history
- Jira integration supports setting Custom Fields on issues. #43 - Aikido Infinite (Continuous Pentesting), VM Reachability Diagrams & IDE full scan · seen Jul 2026 · source · release history
example
-
Attach custom Jira fields (e.g. team or severity tier) when Aikido creates issues, so tickets route correctly without manual editing.
In the Aikido console, go to Integrations > Jira, open your integration settings, and configure 'Custom Fields' with the desired Jira field keys and values.#43 - Aikido Infinite (Continuous Pentesting), VM Reachability Diagrams & IDE full scan · seen Jul 2026 · source -
Automatically route Aikido security findings into ServiceNow for teams that manage remediation through existing ITSM workflows.
In the Aikido console, go to Integrations > Task Trackers > ServiceNow and connect your ServiceNow instance to enable automatic ticket creation from findings.#48 - AI Code Audit, Aikido MCP and ServiceNow Integration · seen Jul 2026 · source
MCP integration shipped suggested Exposes security findings such as leaked secrets and critical vulnerabilities directly to AI coding assistants via the Model Context Protocol.
Suggested capability: Static application security testing. This is our guess, not confirmed.
Also counts toward: MCP server
release 11 total
- Adds ignore, unignore, snooze, and unsnooze tools to the MCP integration. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history
- Adds Devin MCP integration for AI-assisted workflows. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history
- Adds new MCP tools: Get issue details including pentest information, Deep Review, and other SCA scanning tool data. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
- Introduces new MCP tools including Get issue details for pentesting, deep review, and SCA scanning. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · Sep 2026 · source · release history
- New Aikido MCP integration lets AI agents analyze code for security risks and fixes locally, without sending code or data to the cloud. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
- MCP v1.0.8 adds a new search repositories tool. #49 - Visualize Threat models, Device Protection for Windows and Labels on Repositories & Containers · seen Jul 2026 · source · release history
example
-
Query your Aikido security findings — such as leaked secrets or critical open vulnerabilities — directly from an AI coding assistant via the MCP integration.
In your AI coding assistant's MCP settings, add the Aikido MCP server, then prompt: "Show me all critical findings and leaked secrets in the <repo> repository."#48 - AI Code Audit, Aikido MCP and ServiceNow Integration · seen Jul 2026 · source
Package health and malware detection shipped Scores packages for health and detects malware across multiple ecosystems including PHP, Go, Rust, and WordPress plugins.
release 12 total
-
Adds Hugging Face to supported malware ecosystems in Aikido Intel.
#58 - Cloud Security Audits, External Network Pentesting and Aikido is now FedRAMP Moderate · seen Oct 2026
· source
· release history
-
Adds
GET /api/eol-base-data(Get EOL base data) endpoint. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history -
Adds
GET /api/package-healthendpoint to query package health data. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history - Extends Package Health support to Nuget and Jetbrains ecosystems #54 - Device Protection for Linux and VM Scanning for Google Cloud · Aug 2026 · source · release history
-
Adds extension governance covering VS Code, OpenVSX, Chrome, and skills.sh extensions.
🚀 Protect Company Devices From Supply Chain Attacks · seen Aug 2026
· source
· release history
- Package Health adds support for NuGet and JetBrains packages. #54 - Device Protection for Linux and VM Scanning for Google Cloud · seen Aug 2026 · source · release history
Labels and metadata management shipped Lets users attach metadata labels to repositories and container images and filter the issue feed by those labels.
Also counts toward: Import from a competing product, REST API
release 9 total
- New API endpoints to get, add, update, and remove container labels. #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · seen Jul 2026 · source · release history
- Supports importing labels directly from GitHub. #50 - Agentic Dependency AutoFix, Registry Proxy and Device Protection adds Ruby and Rust · seen Jul 2026 · source · release history
- New Labels feature lets you attach arbitrary metadata (business unit, PII, region, etc.) to repositories and container images and filter your issue feed by those labels. #49 - Visualize Threat models, Device Protection for Windows and Labels on Repositories & Containers · seen Jul 2026 · source · release history
- Adds K8s namespaces to container labels #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · Jul 2026 · source · release history
- API now supports managing labels on repositories. #50 - Agentic Dependency AutoFix, Registry Proxy and Device Protection adds Ruby and Rust · seen Jul 2026 · source · release history
- Adds API endpoints to Get, Add, Update, Remove Container label #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · Jul 2026 · source · release history
example
-
Filter your issue feed to only repositories tagged with a specific business unit or data-sensitivity label to prioritize remediation for PII-handling services.
In the Aikido console, go to Repositories (or Container Images) > select a repo > Labels > add a label (e.g. 'PII' or 'business-unit:payments').#49 - Visualize Threat models, Device Protection for Windows and Labels on Repositories & Containers · seen Jul 2026 · source
Automated CVE remediation shipped Applies configurable rules to automatically upgrade, downgrade, snooze, or ignore CVE findings without manual intervention.
release 8 total
-
Enables automated remediation actions — upgrading, downgrading, snoozing, or ignoring findings — driven by user-controlled rules and codebase-aware LLM reasoning.
🚀Extreme Noise Reduction for Secrets and CVEs · seen Aug 2026
· source
· release history
- Adds CVE Exploitability Analysis: an LLM agent that evaluates whether a CVE is practically exploitable given how your codebase uses the affected package, then can automatically upgrade, downgrade, snooze, or ignore the finding. 🚀Extreme Noise Reduction for Secrets and CVEs · seen Aug 2026 · source · release history
- Adds ability to ignore license issues by path. #54 - Device Protection for Linux and VM Scanning for Google Cloud · seen Aug 2026 · source · release history
- Both agents can act autonomously: upgrading, downgrading, snoozing, or ignoring findings automatically based on rules you control. 🚀 Extreme Noise Reduction for Secrets and CVEs · seen Aug 2026 · source · release history
- CVE Exploitability assessment now supports containers. #54 - Device Protection for Linux and VM Scanning for Google Cloud · seen Aug 2026 · source · release history
- Adds Google Cloud Artifact Registry Proxy support. #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · seen Jul 2026 · source · release history
example
-
Use Agentic Dependency AutoFix on a project with many interlocking dependencies to let Aikido automatically compute and apply a safe upgrade path.
In the Aikido console, open a dependency vulnerability finding and select 'AutoFix' to trigger the agentic resolution workflow.#50 - Agentic Dependency AutoFix, Registry Proxy and Device Protection adds Ruby and Rust · seen Jul 2026 · source
Supply chain protection (Safe-Chain) shipped Intercepts package installations across ecosystems and CI environments to block malicious or risky packages before they reach the codebase.
Also counts toward: Scripting language support
release 7 total
-
New Device Protection agent provides real-time malware blocking across npm, PyPI, Maven, and NuGet package managers, powered by Aikido Intel.
🚀 Protect Company Devices From Supply Chain Attacks · seen Aug 2026
· source
· release history
- Safe-Chain adds custom registry support for Python and Jenkins support. #42 - Dep Upgrade Analysis, Eclipse IDE, AI Pentest Preview & Real Time Kubernetes Image Scanning · seen Jul 2026 · source · release history
- Releases new Safe Chain version with minimum package age support for Python. #45 - Aikido × Lovable - Vibe, Fix, Ship and Container Reachability · seen Jul 2026 · source · release history
- Supports group-based policies allowing different installation rules to be set per team. New - Protect Company Devices From Supply Chain Attacks 🚀 · seen Jul 2026 · source · release history
- Safe-chain adds full Python support (pip, pipx, uv, poetry) and CircleCI support, plus configurable custom/private npm registries. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
- New request-and-approval workflow pauses blocked installs and routes one-click exception requests to the admin Inbox inside Aikido. New - Protect Company Devices From Supply Chain Attacks 🚀 · seen Jul 2026 · source · release history
example
-
Review and action a developer's blocked-install exception request without leaving Aikido.
In the Aikido console, go to Device Protection > Inbox, locate the pending approval request, review the flagged package details, and approve or deny the exception.New - Protect Company Devices From Supply Chain Attacks 🚀 · seen Jul 2026 · source
Cloud provider API integration shipped Provides API endpoints to connect cloud provider registries and accounts, including GCP registry integration.
Also counts toward: REST API
release
- Adds an Aikido Terraform provider integration. #53 - Deep Review, Android Pentests, Custom Reports and Free Credits · seen Aug 2026 · source · release history
- New API endpoint to add GCP registry. #46 - Escalating your AI Pentest and Additional Context for AutoTriage · seen Jul 2026 · source · release history
- New API endpoint to add Azure Container Registry. #46 - Escalating your AI Pentest and Additional Context for AutoTriage · seen Jul 2026 · source · release history
- New API endpoint to add a Kubernetes cluster. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
- New API endpoints: save pull request config for Azure, Bitbucket, and GitHub; adjust group severity; add subdomains to attack surface domains. #43 - Aikido Infinite (Continuous Pentesting), VM Reachability Diagrams & IDE full scan · seen Jul 2026 · source · release history
- Adds Azure Management Group support to automatically discover all groups and subscriptions in a single connection #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · Dec 2025 · source · release history
example
-
Connect an Azure Management Group so Aikido automatically discovers all current and future subscriptions without manual re-configuration.
In the Aikido console, go to Integrations > Cloud > Azure, choose 'Management Group', enter your Management Group ID, and save — Aikido will enumerate all child groups and subscriptions automatically.#41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source
Self-hosted broker shipped Supports self-hosted broker deployments via a Helm chart for environments that cannot expose code to external services.
Also counts toward: Kubernetes-native deployment, Self-hosted deployment
release
- Adds Broker management API for programmatic control of broker configuration. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
-
Altar is deployable on a 4-H200s node using
vLLM, with model weights, a model card, license, serving flags, and deployment instructions available under Aikido's organization.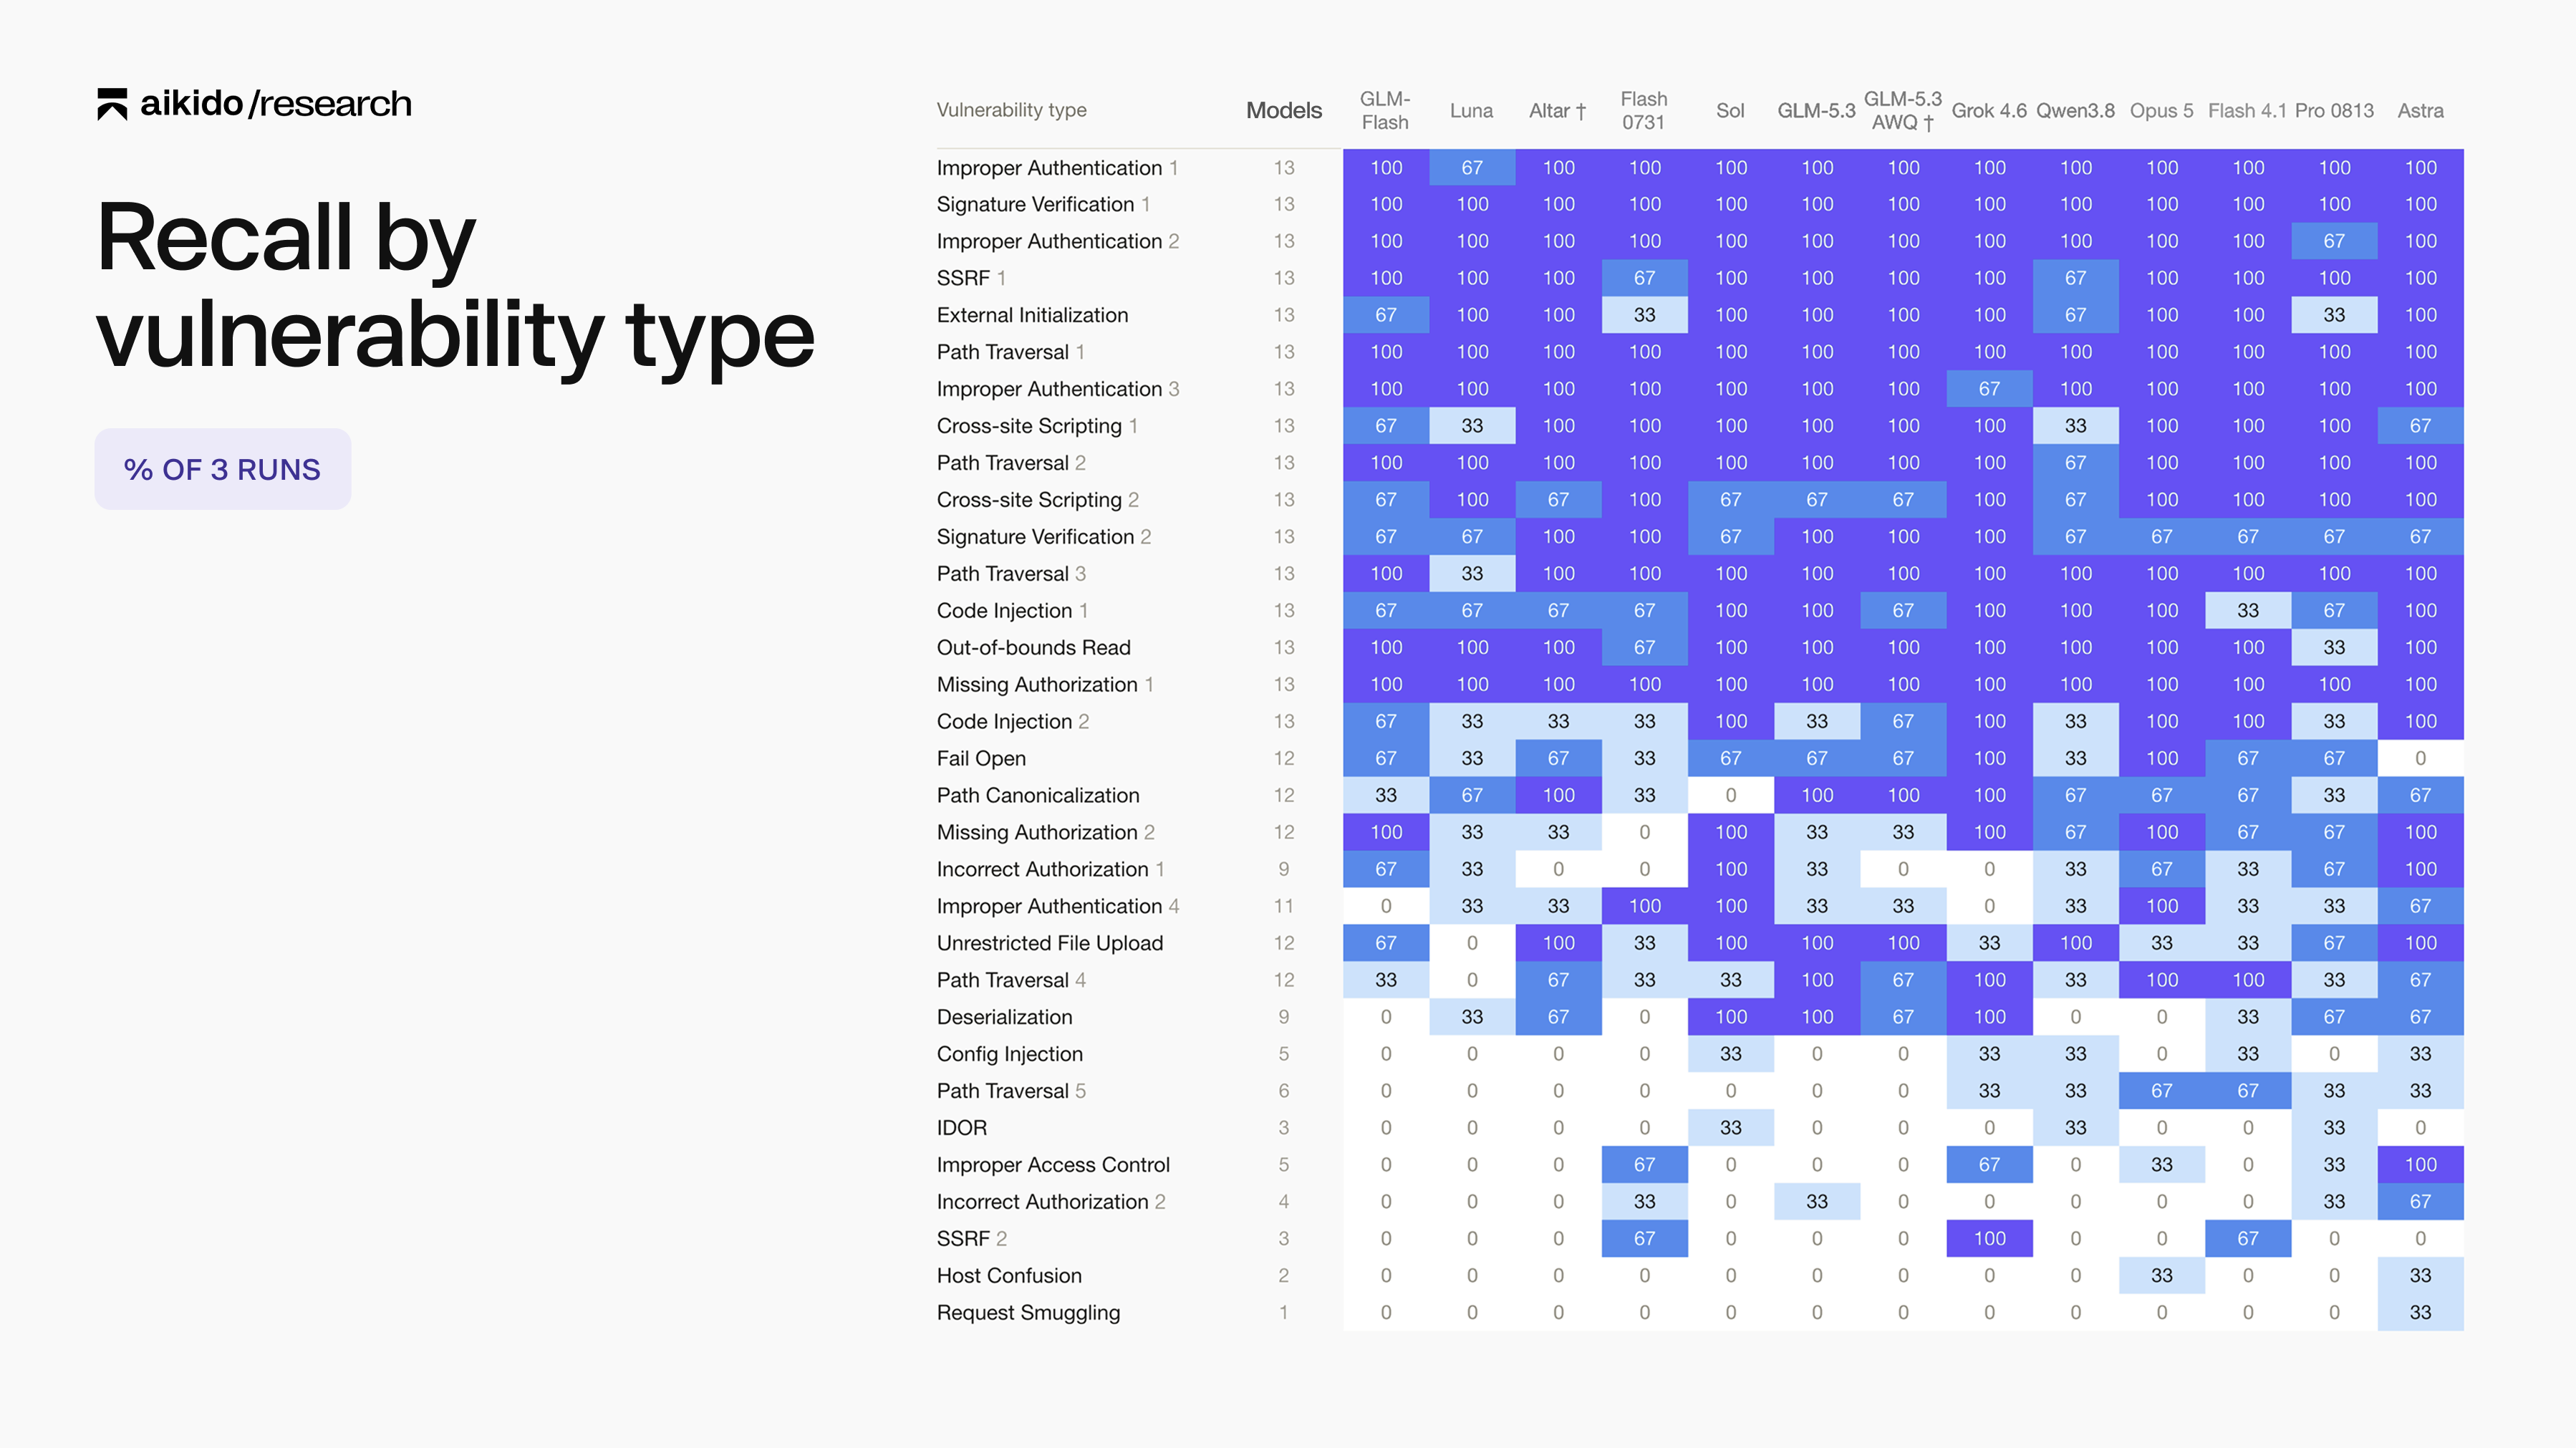 announced · Sep 2026
· source
· release history
- Introduces Altar, an open-weight security AI model (328 GB, W4A16 quantization, 168 of 256 routed experts retained) that powers Aikido Machine's autonomous pentesting entirely inside customer-controlled or air-gapped infrastructure without sending code or findings to a third-party inference… announced · Sep 2026 · source · release history
- New Broker Helm chart released for self-hosted broker deployments. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
- New GitHub Enterprise Server on-premises support via Aikido Broker for code scanning. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
- Adds broker support for WebSockets in integrations. #46 - Escalating your AI Pentest and Additional Context for AutoTriage · seen Jul 2026 · source · release history
API and domain scanning shipped suggested Scans APIs and domains for vulnerabilities, including flows that require authentication or one-time passwords.
Suggested capability: Web vulnerability scanning. This is our guess, not confirmed.
release
- Adds webhook event for when a Domain scan finishes. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
- New OTP/2FA support for authenticated API scanning in Domains & APIs. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
- New custom headers support for API scans in Domains & APIs. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
- New ability to link domains directly to teams in Domains & APIs. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
- Updates headers for the Domain Scan API. #46 - Escalating your AI Pentest and Additional Context for AutoTriage · seen Jul 2026 · source · release history
- Adds API endpoint Add subdomains to attack surface domains. #43 - Aikido Infinite (Continuous Pentesting), VM Reachability Diagrams & IDE full scan · Mar 2026 · source · release history
CIS benchmark reporting shipped Generates CIS and AWS CIS compliance reports accessible via the API.
release
-
Adds new API endpoints:
API - List CWE descriptionsto retrieve CWE metadata,API - List pending invitesto query outstanding user invitations,API - List AI code analysis assessmentsto fetch AI code analysis results,API - List pentest assessmentsto retrieve pentest findings,API - Disable userto…
#58 - Cloud Security Audits, External Network Pentesting and Aikido is now FedRAMP Moderate · seen Oct 2026
· source
· release history
-
Adds
API - Report export for PCI and DORA complianceendpoint to export compliance reports programmatically. #55 - Code Coverage for Github, SIEM Integrations and Pentest for AI capabilities · seen Sep 2026 · source · release history - New API endpoint: Get CIS and AWS CIS report. #47 - Aikido Device Protection and Aikido AI Chat · seen Jul 2026 · source · release history
- New Reports: UK Cyber Essentials. #42 - Dep Upgrade Analysis, Eclipse IDE, AI Pentest Preview & Real Time Kubernetes Image Scanning · seen Jul 2026 · source · release history
- New CIS Kubernetes Benchmark report available. #49 - Visualize Threat models, Device Protection for Windows and Labels on Repositories & Containers · seen Jul 2026 · source · release history
- New FDA/NTIA-compliant reports with component hashes and supplier information. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
AI Pentest assessment reporting shipped Provides detailed AI pentest assessment results accessible programmatically via the API.
Also counts toward: REST API, Scripting API
release
-
Every pentest produces an audit-ready report with validated findings, proof of exploit, and remediation guidance suitable for compliance and auditor review.
announced · Oct 2026
· source
· release history
-
Adds new API endpoints:
API - List CWE descriptionsto retrieve CWE metadata,API - List pending invitesto query outstanding user invitations,API - List AI code analysis assessmentsto fetch AI code analysis results,API - List pentest assessmentsto retrieve pentest findings,API - Disable userto…
#58 - Cloud Security Audits, External Network Pentesting and Aikido is now FedRAMP Moderate · seen Oct 2026
· source
· release history
- New API endpoint to get AI Pentest assessment details. #42 - Dep Upgrade Analysis, Eclipse IDE, AI Pentest Preview & Real Time Kubernetes Image Scanning · seen Jul 2026 · source · release history
- AI Pentest supports programmatic creation of new pentests via API. #42 - Dep Upgrade Analysis, Eclipse IDE, AI Pentest Preview & Real Time Kubernetes Image Scanning · seen Jul 2026 · source · release history
- New API endpoint to get AI Pentest issue details. #44 - Talk to Aikido Autofix, Pentest Threat Model and support for Alibaba Cloud · seen Jul 2026 · source · release history
Governance, Risk, and Compliance (GRC) shipped Integrates with GRC platforms to support compliance workflows.
release
- Aikido AI Pentest findings and compliance evidence sync directly into Drata, eliminating manual spreadsheet exports for audit prep.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Oct 2026 · source · release history
-
Adds
GETList user logins history API endpoint for auditing authentication activity.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history - New Comp AI integration for Governance, Risk, and Compliance (GRC). #43 - Aikido Infinite (Continuous Pentesting), VM Reachability Diagrams & IDE full scan · seen Jul 2026 · source · release history
- New compliance integration with CompAI. #42 - Dep Upgrade Analysis, Eclipse IDE, AI Pentest Preview & Real Time Kubernetes Image Scanning · seen Jul 2026 · source · release history
- Adds Comp AI integration for Governance, Risk, and Compliance. #43 - Aikido Infinite (Continuous Pentesting), VM Reachability Diagrams & IDE full scan · Mar 2026 · source · release history
Custom Reports shipped Lets users describe a report in plain language and have an AI agent build and share it from the findings data.
Also counts toward: Built-in AI assistant, Natural-language query
release
- Adds support for grouped bar charts in Custom Reports. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
-
Each run produces a recon report and attack plan with diagrams, threat scenarios, and the full agent reasoning trace, including vulnerabilities attempted but not confirmed.
announced · Aug 2026
· source
· release history
- New Custom Reports capability lets users describe a report in plain language; Aikido Agent builds it from findings and makes it shareable across the workspace. #53 - Deep Review, Android Pentests, Custom Reports and Free Credits · seen Aug 2026 · source · release history
- Adds a repository filter for trends-over-time in Reports. #53 - Deep Review, Android Pentests, Custom Reports and Free Credits · seen Aug 2026 · source · release history
- Adds Custom Reports via Aikido Agent: users describe the report in plain language and share it with their workspace directly. #53 - Deep Review, Android Pentests, Custom Reports and Free Credits · Aug 2026 · source · release history
Virtual machine scanning shipped suggested Scans virtual machines for vulnerabilities using a local scanner.
Suggested capability: Credentialed vulnerability scanning. This is our guess, not confirmed.
release
- GCP VM Scanning is now generally available — agentless setup with no SSH keys or agents required, completing coverage across AWS, Azure, and GCP. #54 - Device Protection for Linux and VM Scanning for Google Cloud · seen Aug 2026 · source · release history
- Enables agentless Google Cloud VM scanning for all users, requiring no SSH keys or agents #54 - Device Protection for Linux and VM Scanning for Google Cloud · Aug 2026 · source · release history
- Adds GCP support for VM scanning. #48 - AI Code Audit, Aikido MCP and ServiceNow Integration · seen Jul 2026 · source · release history
- New local scanner release for Virtual Machines. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
- Adds GCP VM Scanning support #48 - AI Code Audit, Aikido MCP and ServiceNow Integration · Jun 2026 · source · release history
Ignore request approval workflow shipped Routes team requests to ignore findings through an admin approval inbox before issues are suppressed, maintaining oversight over noise-reduction decisions.
release
- Adds ability to request ignore of an issue on a PR/MR with admin approval. #54 - Device Protection for Linux and VM Scanning for Google Cloud · seen Aug 2026 · source · release history
- New Approval Inbox for Ignores: routes every ignore request through a central inbox requiring admin sign-off before issues leave the feed. #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · seen Jul 2026 · source · release history
- Adds Approval Inbox for Ignores to route ignore requests through admin sign-off #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · Jul 2026 · source · release history
-
Adds a request-and-approval workflow where blocked installs trigger a one-click exception request reviewed in the Aikido Inbox.
🚀 Protect Company Devices From Supply Chain Attacks · May 2026
· source
· release history
example
-
Review and approve or reject team ignore requests before they take effect, maintaining admin control over noise suppression.
In the Aikido console, go to the Approval Inbox and review pending ignore requests submitted by team members before approving or rejecting each.#51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · seen Jul 2026 · source
Registry Proxy shipped Routes package traffic through a private registry proxy that scans for malware and serves safe or patched versions.
release
-
Group-based policies enable different install rules per team.
🚀Protect Company Devices From Supply Chain Attacks · seen Aug 2026
· source
· release history
- Supports group-based policies, enabling different package and extension rules per team. 🚀 Protect Company Devices From Supply Chain Attacks · seen Aug 2026 · source · release history
- Supports Google Cloud Artifact Registry Proxy #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · Jul 2026 · source · release history
- New Registry Proxy routes your private registry through Aikido to block malware and risky new packages and serve safe, patched versions before they reach your codebase. #50 - Agentic Dependency AutoFix, Registry Proxy and Device Protection adds Ruby and Rust · seen Jul 2026 · source · release history
- Package Proxy adds malware scanning for private registries. #49 - Visualize Threat models, Device Protection for Windows and Labels on Repositories & Containers · seen Jul 2026 · source · release history
Notifications and alerting shipped Delivers security finding notifications via email and Slack, with direct actions available from within the notifications.
release
- Adds SIEM Integrations supporting 11 SIEMs, enabling Aikido issues to be forwarded and correlated with other organizational security data. #55 - Code Coverage for Github, SIEM Integrations and Pentest for AI capabilities · seen Sep 2026 · source · release history
- New email forwarding support for Notifications. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
- Slack integration updated with direct actions from Slack notifications and an improved detail view. #43 - Aikido Infinite (Continuous Pentesting), VM Reachability Diagrams & IDE full scan · seen Jul 2026 · source · release history
- New out of SLA graph added to Reports Trends Over Time view. #46 - Escalating your AI Pentest and Additional Context for AutoTriage · seen Jul 2026 · source · release history
- Adds direct actions and improved detail views in Slack alerts. #43 - Aikido Infinite (Continuous Pentesting), VM Reachability Diagrams & IDE full scan · Mar 2026 · source · release history
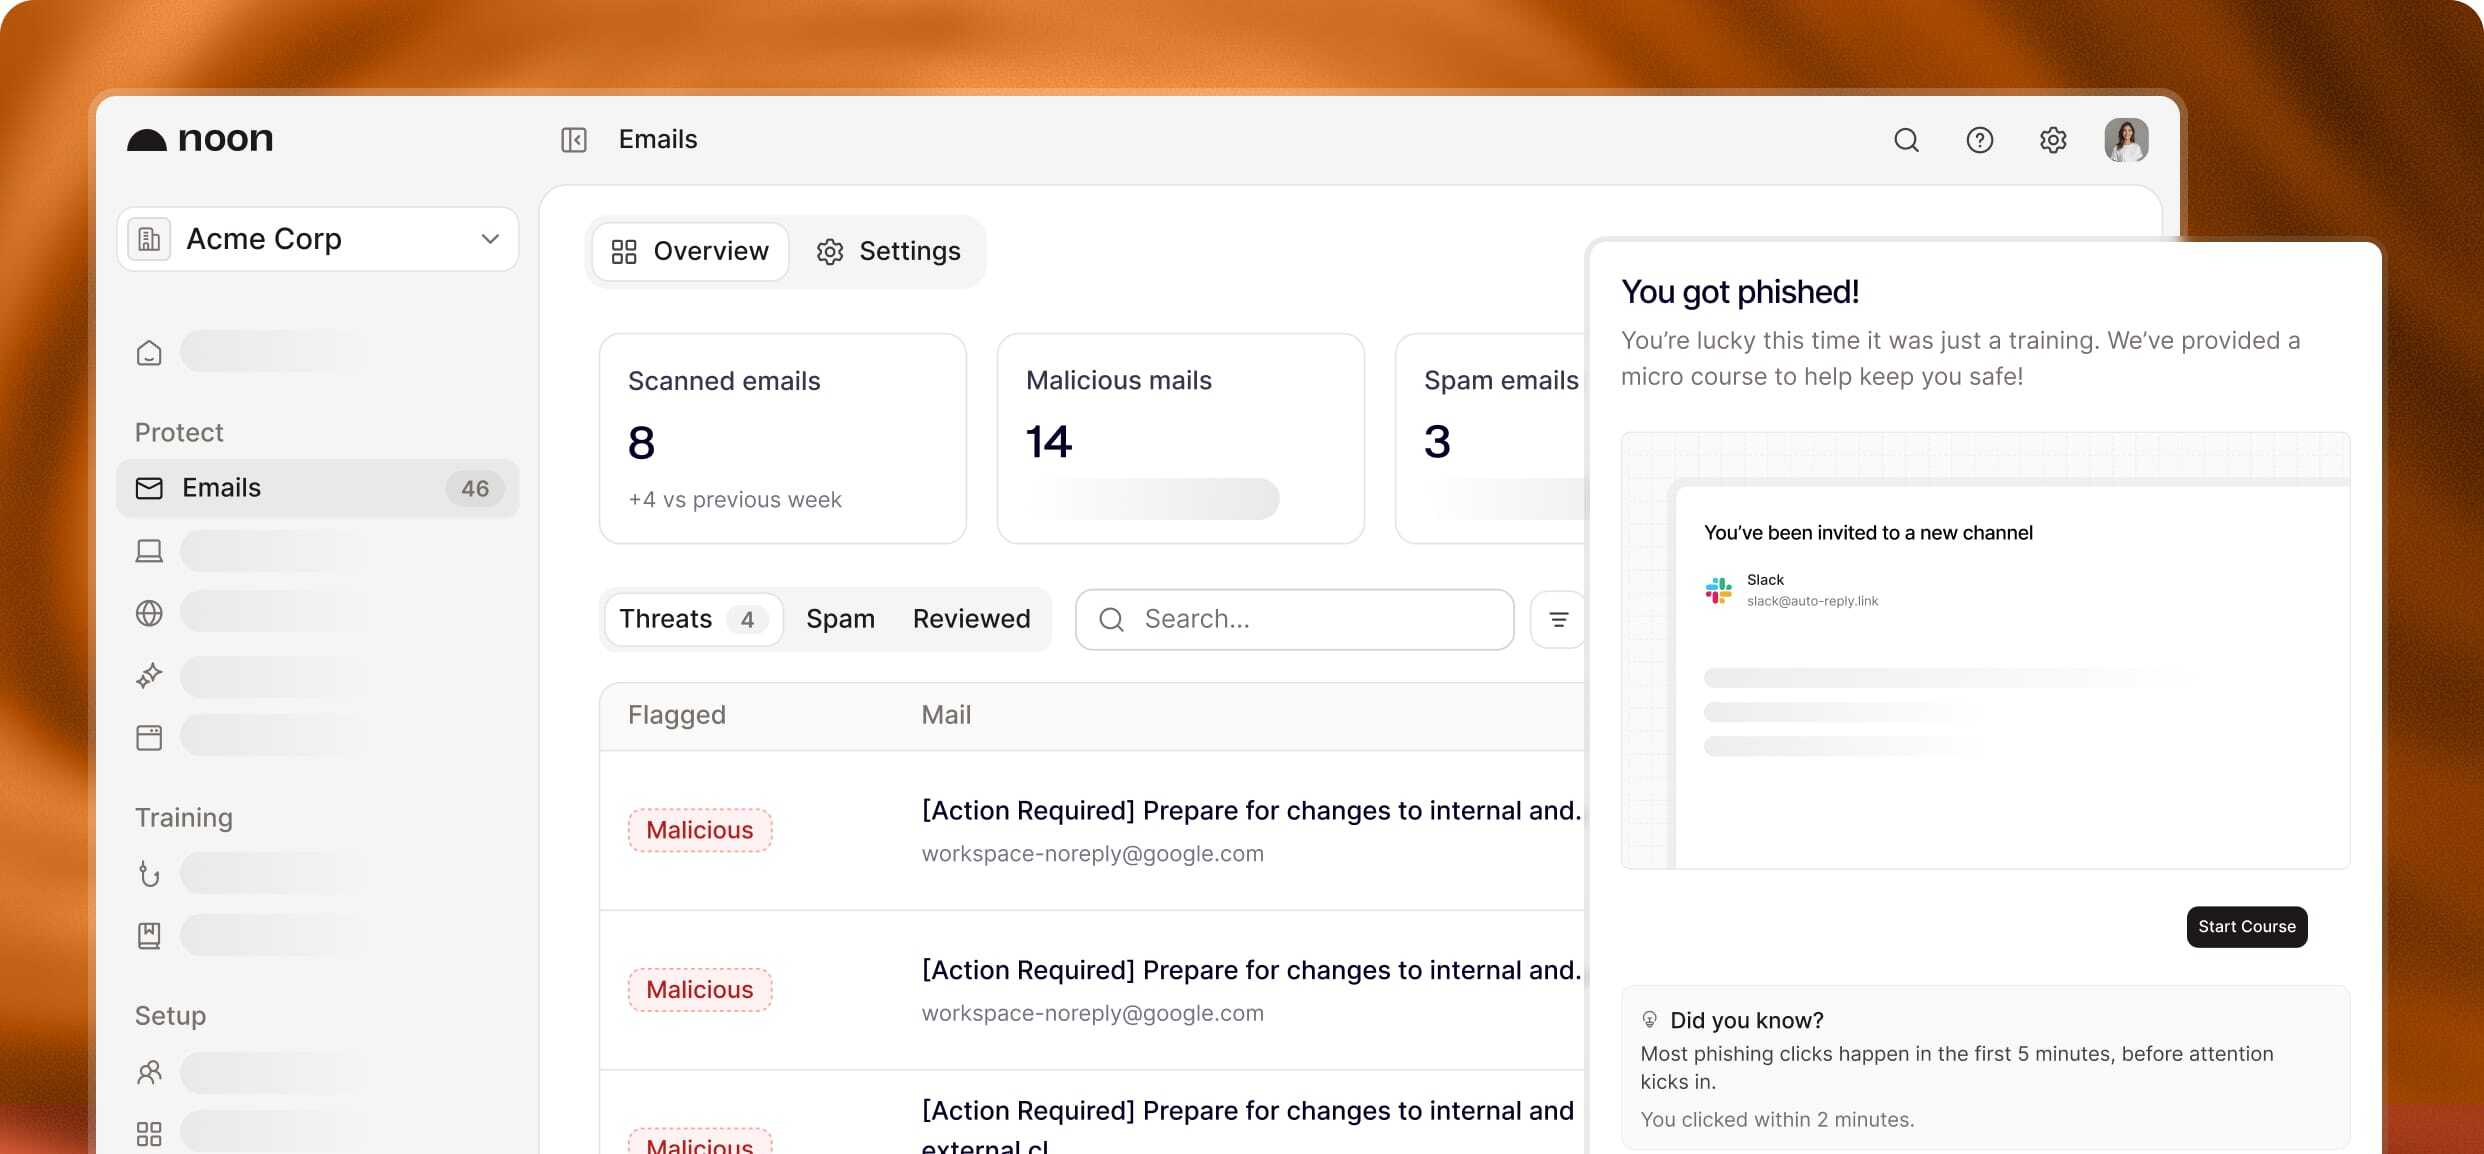
Workforce security platform (Noon) shipped A separate workforce-focused platform combining email threat detection and removal, employee device protection against malicious installs and risky content, AI governance, and role-personalized phishing/vishing/smishing/deepfake training delivered via Slack, Teams, or Google Chat.
Also counts toward: ML-based detection
release
-
Noon's training and simulations module delivers realistic phishing, vishing, smishing, and deepfake attack scenarios personalized by role, behavior, and risk, with lessons delivered in Noon or directly in Slack, Teams, or Google Chat.
 announced · Oct 2026
· source
· release history
- Noon's email security module autonomously detects and removes inbox threats and malicious emails that traditional filters miss. announced · Oct 2026 · source · release history
- Noon's device protection module covers employee devices against malicious packages, installs, extensions, agent skills, AI tools, risky websites, and apps. announced · Oct 2026 · source · release history
- Introduces Noon, a new workforce security platform separate from Aikido's existing developer-focused tooling, combining email security, device protection, AI governance, and phishing training in one product.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Oct 2026 · source · release history
Android Pentest agent shipped Automatically penetration-tests native and hybrid Android apps using real APKs, covering OWASP Mobile Top 10 with exploit confirmation via ADB.
release
-
Supports simultaneous assessment of the Android app and its backend API in a single run — API findings appear in the same report as app findings.
announced · Aug 2026
· source
· release history
- New Android (APK) pentest capability: agents install a real APK on a test device, log in as a user, and attack the app over ADB — findings are exploit-confirmed before appearing in the report. announced · Aug 2026 · source · release history
- Reproduction steps for every finding include the exact ADB commands needed to replay the exploit. announced · Aug 2026 · source · release history
- Adds Android Pentest capability covering native and hybrid Android apps, including those with biometric login. #53 - Deep Review, Android Pentests, Custom Reports and Free Credits · Aug 2026 · source · release history
Threat model visualization shipped Generates architecture diagrams showing roles, trust boundaries, and network paths as part of pentest and code audit reports.
release
- New threat model visualization: every AI pentest and code audit now ships an architecture diagram showing roles and trust boundaries. #49 - Visualize Threat models, Device Protection for Windows and Labels on Repositories & Containers · seen Jul 2026 · source · release history
- New Pentest Threat Model provides a real-time, transparent view of your attack surface and how your application's security posture will be tested. #44 - Talk to Aikido Autofix, Pentest Threat Model and support for Alibaba Cloud · seen Jul 2026 · source · release history
- Every AI pentest & code audit now ships a diagram of your app's architecture, roles, and trust boundaries #49 - Visualize Threat models, Device Protection for Windows and Labels on Repositories & Containers · Jun 2026 · source · release history
- Adds Pentest Threat Model providing a real-time view of attack surface and testing posture. #44 - Talk to Aikido Autofix, Pentest Threat Model and support for Alibaba Cloud · Mar 2026 · source · release history
Cloud rules management shipped Allows the rules used for cloud security scanning to be listed and managed via the API.
Also counts toward: REST API
release
- New API endpoint: List Cloud rules. #47 - Aikido Device Protection and Aikido AI Chat · seen Jul 2026 · source · release history
- Adds List Cloud rules API endpoint. #47 - Aikido Device Protection and Aikido AI Chat · May 2026 · source · release history
Dashboard shipped Provides a dashboard giving all users a summary view of current security findings and their status.
release
- Adds UI localisation in Spanish, Portuguese, Japanese, French, and German across the platform. #57 - Aikido speaks 5 languages and adds a Terraform provider · seen Oct 2026 · source · release history
- New Dashboard available to all users. #51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · seen Jul 2026 · source · release history
Issue annotation shipped Allows users to add notes to issue groups to record context and decisions alongside findings.
Also counts toward: REST API
release
- New API endpoint to add a note to an issue group. #41 - Aikido MCP, re-testing AI Pentest findings, and Azure Management Group support · seen Jul 2026 · source · release history
example
-
Review and approve or reject team ignore requests before they take effect, maintaining admin control over noise suppression.
In the Aikido console, go to the Approval Inbox and review pending ignore requests submitted by team members before approving or rejecting each.#51 - Repository Code Quality scans, Ignore Approval Inbox and Noise Reduction for Secrets & CVE’s · seen Jul 2026 · source
SIEM integration shipped Forwards Aikido activity logs to external SIEM platforms, with Google SecOps as the first supported destination, for centralized alerting and correlation.
Also counts toward: SIEM forwarding
release
-
New Google SecOps integration to optionally forward Aikido Activity logs to a SIEM.
#58 - Cloud Security Audits, External Network Pentesting and Aikido is now FedRAMP Moderate · seen Oct 2026
· source
· release history
example
-
Forward Aikido Activity logs to Google SecOps for centralized SIEM alerting and correlation.
Steps: In Aikido, go to Settings > Integrations > SIEM, enable 'Transmit Activity logs', and select 'Google SecOps' as the destination.#58 - Cloud Security Audits, External Network Pentesting and Aikido is now FedRAMP Moderate · seen Oct 2026 · source
Cloud inventory mapping shipped Maps cloud resources by region and VPC with exposure findings and firewall rules accessible in one click.
release
- Introduces Cloud Inventory (Cloud Asset Map): see every cloud resource laid out by region and VPC, with exposure findings and firewall rules accessible in one click. #56 - Cloud Asset Map, Creating fix PRs with Deep Review and Code Coverage on GitLab · seen Sep 2026 · source · release history
FedRAMP authorization shipped Aikido for Government holds FedRAMP Moderate authorization and is listed on the FedRAMP Marketplace, enabling federal agencies to adopt the platform without conducting a full security review.
release
-
Aikido for Government achieves FedRAMP Moderate authorization and is listed on the FedRAMP Marketplace, allowing federal agencies to adopt Aikido without a full security review.
#58 - Cloud Security Audits, External Network Pentesting and Aikido is now FedRAMP Moderate · seen Oct 2026
· source
· release history
FIPS-compliant Kubernetes agents shipped Provides FIPS-variant agents for Kubernetes deployments that require FIPS-compliant cryptography.
release
- Kubernetes agents now have FIPS variants. #53 - Deep Review, Android Pentests, Custom Reports and Free Credits · seen Aug 2026 · source · release history
Training mode PR bypass shipped Allows PR check enforcement to be bypassed on a per-repository basis when a repository is in Training mode.
release
- Adds per-repository bypass of PR checks in Training mode. #53 - Deep Review, Android Pentests, Custom Reports and Free Credits · seen Aug 2026 · source · release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for Aikido Security, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Aikido Security puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Commercials
pricing & packaging history · Aikido Security vendor page30 readings of Aikido Security's pricing page since Mar 2023, with 13 relaunches of its plan lineup and 15 changes to what its plans include — each one dated, compared with the reading before it, and explained for someone buying the tool.
Pricing and packaging history is included with Researcher and Business. See how every vendor we track sells, and how that has changed over time, using data we don't publish anywhere else.
See plans → Already subscribed? Sign in →Plans by offering
Each offering on the pricing page links to its own page of plans, read at its latest capture.
Plan relaunches
Plans, prices and descriptions are quoted from the vendor's own pricing page as we read it on each date. A plan missing from a later reading is shown as no longer listed on the page — a statement about the page, not the product. Readings that failed to show any plans are left out rather than read as a change.
Website history
aikido.dev, every changeAikido Security's home, pricing and product pages and 40 more pages as they looked each month from December 2022 to October 2026: 122 renders, 19 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Coverage
Missing something? Tell us
What Aikido Security connects to, runs on and detects, read from its release notes and docs. So far: 1 new integration.
1 change, tracked since Oct 19, 2026.
-
Oct 192026
new Aikido AI Pentest integration with Drata
With SOC 2, ISO 27001, PCI DSS, DORA, HIPAA
Aikido runs the checks and generates the evidence behind Drata's technical controls, including SOC 2, ISO 27001, PCI DSS (Payment Card Industry Data Security Standard), DORA (the EU's Digital Operational Resilience Act), and HIPAA. Findings, and the evidence behind them, sync into Drata without anyone exporting a spreadsheet.
Observability & monitoring 1
Other 5
Nothing first seen in this window. That doesn't mean Aikido Security shipped nothing, only that we found no record of it.
How we count
Read from 2 of 73 release notes and docs updates we hold for Aikido Security. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through Aikido Security's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
73 entries
No entries match these filters.
- October 20267
- September 202610
- August 202625
- July 202619
- June 20263
- May 20263
- April 20262
- March 20262
- February 20261
- December 20251
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →