Belkasoft
Belkasoft X 2.11: A Sneak Peek (2026-05-21) commercialThe section your link pointed to isn't on Belkasoft's page any more, so we've brought you to the top.
Belkasoft is a digital forensics and incident responsedigital forensics and incident responseDigital forensics and incident response, investigating what happened during a security incident and containing it. The work includes preserving evidence, reconstructing activity and restoring systems. platform for investigating cybercrime, data breaches, and security incidents.
Summary
Belkasoft is a commercial digital forensics suite, sold as Belkasoft X, that acquires and analyzes evidence from phones, computers, cloud accounts, drones, and cars for a single investigation. It runs as a desktop application on forensic workstations rather than as a hosted service, with an offline AI assistant (BelkaGPT) and map server available for air-gapped labs. It is built for DFIRDFIRDigital forensics and incident response, investigating what happened during a security incident and containing it. The work includes preserving evidence, reconstructing activity and restoring systems. practitioners: in-house corporate and cyber security teams, law enforcement and government agencies, and academic programs training investigators, with separate editions for corporate incident response and eDiscoveryeDiscoveryA legal process for identifying, collecting, and producing electronically stored information in response to litigation or investigation; cyber tools integrate with it to extract and preserve forensic evidence in legally defensible formats. work. Recent capabilities include SQLite database classification, custom artifact mapping for unsupported databases, offline translation across 200+ languages, and expanded mobile passcode brute-forcing across additional MediaTek chipsets.
Belkasoft is a digital forensics and incident response platform for investigating cybercrime, data breaches, and security incidents.
How Belkasoft helps
What did a suspect do on this device, and when?
reconstructs activity from parsed artifacts across mobile, computer, and cloud sources — chats, call logs, browsing, application usage, event logs — and lines them up with timestamps for a single timeline of the case
Can I get into this locked phone without the passcode?
runs a brute-force attack against supported iPhone, iPad, and Android models, including dictionary-based and unknown-length attacks on certain chipsets, to unlock the device before acquisition
What does this unfamiliar or proprietary database on the device actually contain?
scans the SQLite file's contents and assigns it categories such as communications, locations, financial information, or credentials, so it can be triaged without a dedicated parser
Where was this device when these messages were sent?
plots extracted geolocation evidence on a map, including one hosted entirely inside the lab for cases that cannot touch an online mapping service
What did this remote desktop session actually show on screen?
rebuilds Windows Remote Desktop bitmap cache tiles and stitches visually matching fragments into larger image sequences for review
What was installed, run, or connected on this Windows machine, and when?
pulls Background/Desktop Activity Moderator, SRUM, and System Event Log data and groups related events into categories like logons, installs, remote access, and Wi-Fi connections
Languages
Features
Built from Belkasoft's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- Belkasoft covers 1 of the 8 investigation and response capabilities we track.
- Belkasoft covers 1 of the 11 endpoint investigation and controls capabilities we track.
What Belkasoft offers you
- Offline mode3
- Built-in AI assistant1
- Command-line interface1
- Self-hosted deployment1
No capabilities match.
Disk and filesystem forensics 5 features Investigation and response since 2026
Extended Android acquisition surface shipped Expands the platform's evidence collection surface with new acquisition methods for mobile devices.
Shared capability: Disk and filesystem forensics
release
-
Supports adding MTK dumps acquired externally with MTKClient as a Mobile image data source in Belkasoft X, after converting extracted encryption keys to the supported format via Belkasoft Support.
 announced · Oct 2026
· source
· release history
- Adds MTK dump acquisition method in Belkasoft X for physical imaging of Android devices based on 23 supported MediaTek chipsets (MT3369, MT6731, MT6737, MT6739, MT6761, MT6762, MT6763, MT6765, MT6768, MT6769, MT6853, MT6873, MT6877, MT6880, MT6883, MT6885, MT6889, MT6890, MT6893, MT8765, MT8785, MT8766B, MT8768t)… announced · Oct 2026 · source · release history
-
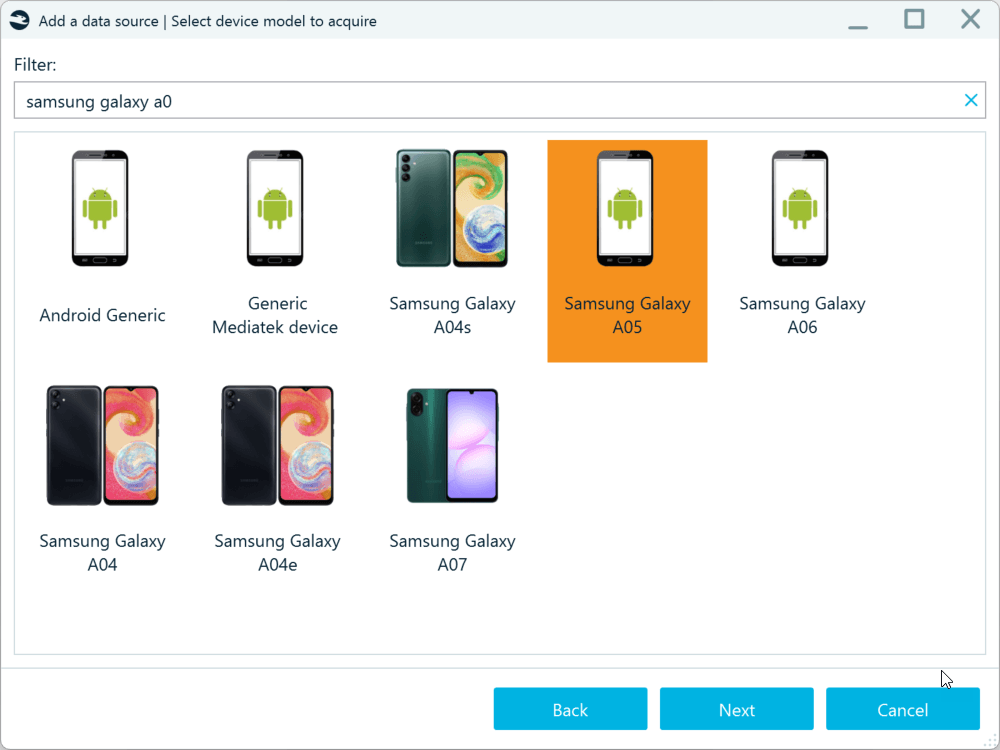
Supports Generic Mediatek device selection and chipset-name search (e.g.
MT6769) when the exact device model is not listed in the supported-device list. announced · Oct 2026 · source · release history - Adds new acquisition methods to expand the platform's evidence collection surface. Belkasoft X 2.11: A Sneak Peek (2026-05-21) · May 2026 · source · release history
Extended BAM/DAM artifact extraction shipped Extends Background Activity Moderator and Desktop Activity Moderator extraction to Windows 10 version 1809 and later.
Shared capability: Disk and filesystem forensics
release
- Extends BAM/DAM artifact extraction to Windows 10 version 1809 and later, capturing executable paths and timestamps from Background Activity Moderator and Desktop Activity Moderator data. announced · Sep 2026 · source · release history
docs
-
Analyzing Windows BAM and DAM with Belkasoft X
https://belkasoft.com/bam-dam-analysisbelka_site_2313 Fri, 02 Oct 2026 16:31:17 GMT seen Oct 2026 · source
MediaTek userdata decryption support shipped Decrypts userdata partitions on file-based encryption-protected devices using cryptographic material extracted during BootROM-mode acquisition.
Shared capability: Disk and filesystem forensics
release
-
Adds decryption of the
userdatapartition from acquired MTK dumps, supporting file-based encryption (FBE) protected devices by extracting cryptographic material obtained during BootROM-mode acquisition.
announced · Oct 2026
· source
· release history
Remote Desktop Cache reconstruction shipped Extracts Windows Remote Desktop bitmap cache tiles and automatically combines visually matching fragments into larger image sequences.
Shared capability: Disk and filesystem forensics
release
- Adds Remote Desktop Cache reconstruction: extracts Windows Remote Desktop bitmap cache tiles and automatically combines visually matching fragments into larger image sequences for examination. announced · Sep 2026 · source · release history
Apple Biome forensics support documented Adds support for extracting and analyzing Apple Biome artifacts, including their locations and the SEGB format.
Shared capability: Disk and filesystem forensics
docs
-
Apple Biome Forensics: Artifacts, Locations, and SEGB format
https://belkasoft.com/biome-forensics-artifactsbelka_site_2310 Fri, 25 Sep 2026 10:07:52 GMT seen Sep 2026 · source
Remote forensic collection 1 feature Endpoint investigation and controls since 2026
Expanded Android agent-based acquisition shipped Supports USB flash drives via USB-C adapters, custom folder selection, and improved reliability for SMS and call history on recent Android versions.
Shared capability: Remote forensic collection
release
- Expands Android agent-based acquisition (Agent backup via SD card method) to support USB flash drives via USB-C adapters, custom folder selection on device or external media, and improved reliability on recent Android versions with added SMS and call history collection. announced · Sep 2026 · source · release history
Other / not yet classified 13 features Features we have not matched to a capability yet. A suggested match is marked.
Mobile passcode brute-force shipped suggested Recovers passcodes on locked iOS and Android devices during forensic investigations using a brute-force module.
Suggested capability: Disk and filesystem forensics. This is our guess, not confirmed.
release
-
Adds offline brute-force passcode recovery for MTK devices through the Brute-force options dialog, with three attack modes: built-in Belkasoft dictionary (4- and 6-digit numeric passcodes), sequential numeric brute-force (0000 through 11-digit combinations), and a custom User dictionary supplied as a
.txtfile…
announced · Oct 2026
· source
· release history
- Redesigns the MTK Dump acquisition workflow, separating acquisition and decryption into independent operations and adding passcode brute-force with unknown-length support, dictionary-based alphanumeric attacks, and new chipset support: MT3369, MT6762, MT6880, MT6883, MT6889, MT6890, MT8765, MT8766B, and MT8768T. announced · Sep 2026 · source · release history
docs
- MT3369, MT6731, MT6737, MT6739, MT6761, MT6762, MT6763, MT6765, MT6768, MT6769, MT6853, MT6873, MT6877, MT6880, MT6883, MT6885, MT6889, MT6890, MT6893, MT8765, MT8785, MT8766B, MT8768t seen Oct 2026 · source
- Mobile Passcode Recovery Unlock supported iOS and Android devices during forensic investigations with Belkasoft X's Mobile Passcode Brute-Force module. docs update · Aug 2026 · source
example
-
Recover an alphanumeric passcode on a seized MediaTek device using a custom candidate list built from case intelligence.
1. After adding the MTK dump as a 'Mobile image' and selecting 'userdata', open the 'Brute-force options' dialog. 2. Select 'Run brute-force', then choose 'User dictionary'. 3.announced · Oct 2026 · source -
Acquire a physical image from a MediaTek device whose exact model is unlisted, then brute-force an unknown numeric passcode offline without device lock-screen delays.
1. In Belkasoft X, start a new Android acquisition and search for the chipset by name (e.g. 'MT6769'), or select 'Generic Mediatek device' if unsure. 2.announced · Oct 2026 · source -
Acquire a MediaTek device and defer decryption until a passcode is obtained or a dictionary attack can be staged.
In the MTK Dump acquisition workflow, run acquisition to capture the raw dump, then return to the saved dump later and select 'Decrypt user data partition' — entering a known passcode or launching a…announced · Sep 2026 · source
AI-powered SQLite classification shipped suggested Automatically scans database contents to assign categories for triage of unfamiliar or proprietary databases without a dedicated parser.
Suggested capability: Disk and filesystem forensics. This is our guess, not confirmed.
release
- Adds BelkaGPT-powered SQLite database classification that scans database contents and assigns predefined categories (communications, locations, financial information, credentials) or custom user-defined categories, enabling triage of unfamiliar or proprietary databases without a dedicated parser. announced · Sep 2026 · source · release history
docs
- This new feature is especially useful with unfamiliar or proprietary applications for which Belkasoft X does not yet have a dedicated parser. seen Sep 2026 · source
-
September 2026 Belkasoft X v2.12 is here with one of the broadest sets of updates in recent releases. It adds offline evidence translation, AI-powered SQLite classification, custom SQLite artifacts, and easier BelkaGPT Hub deployment.
 docs update · Sep 2026
· source
Offline evidence translation shipped Provides offline, locally processed bulk translation of chats and messages via AI directly within the artifact review workflow.
Also counts toward: Offline mode
release
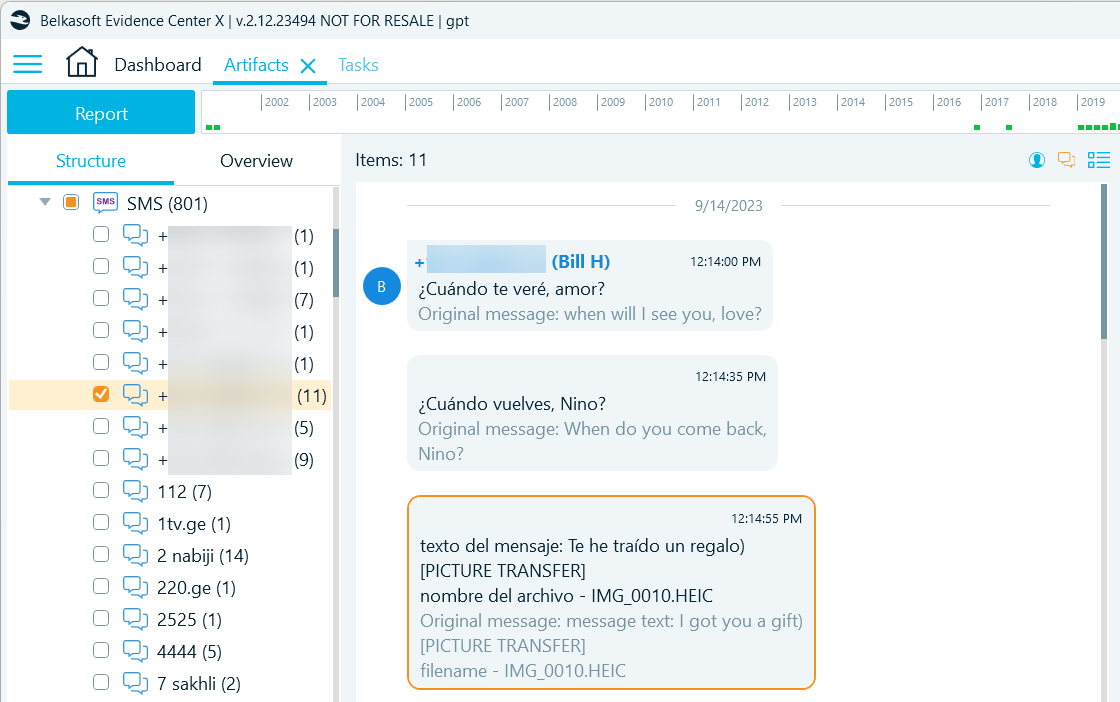
- Adds offline evidence translation via BelkaGPT directly within the artifact review workflow, supporting bulk translation of chats and SMS, per-message translation, translated message search, and report inclusion — covering 200+ source languages into 100+ target languages, all processed locally. announced · Sep 2026 · source · release history
docs
-
Translation to (from 200+ auto-detected languages and dialects)
 docs update · Sep 2026
· source
example
-
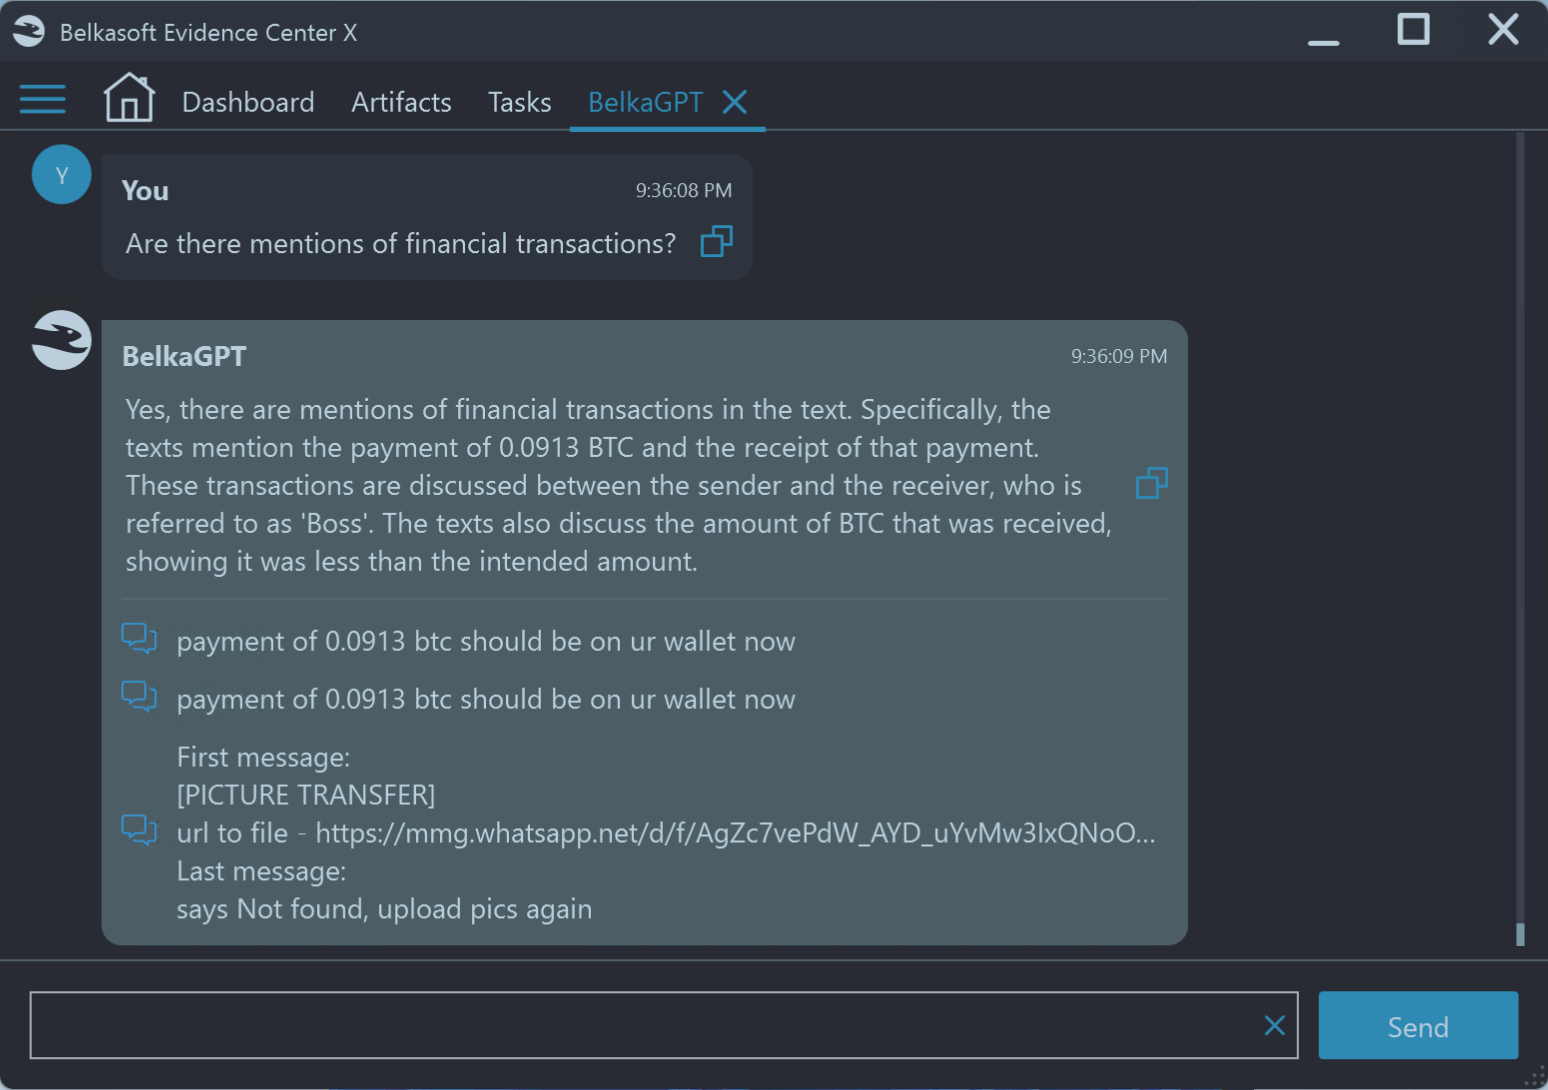
Use BelkaGPT in the UI to query multilingual evidence and summarize large datasets faster.
In the Belkasoft X console, open the BelkaGPT panel and input your case dataset for analysis.Belkasoft X 2.11: A Sneak Peek (2026-05-21) · May 2026 · source
Offline map server shipped Provides a locally deployed map server for reviewing geolocation evidence without connecting forensic workstations to online mapping services.
Also counts toward: Offline mode
release
- Adds Belkasoft Offline Map Server, a locally deployed map server for reviewing geolocation evidence without connecting forensic workstations to online mapping services; configured by specifying its network address in Belkasoft X settings. announced · Sep 2026 · source · release history
docs
- Belkasoft Offline Map Server docs update · Sep 2026 · source
Distributed offline AI processing deployment shipped Simplifies deployment of offline AI processing to GPU-equipped workstations and servers in a local network.
Also counts toward: Built-in AI assistant, Offline mode, Self-hosted deployment
release
-
New
BelkaGPT Hub installer for Windowssimplifies deployment of distributed offline AI processing to GPU-equipped workstations and servers in a local network, with selectable GPU and CPU resources. announced · Sep 2026 · source · release history - Introduces BelkaGPT, an AI-driven assistant designed to analyze large data volumes and multilingual evidence in cyber tooling workflows. Belkasoft X 2.11: A Sneak Peek (2026-05-21) · May 2026 · source · release history
Command-line automation documented suggested Provides documentation and support for corporate endpoint triage and command-line automation workflows.
Suggested capability: Remote forensic collection. This is our guess, not confirmed.
Also counts toward: Command-line interface
docs
- How Command-Line Automation Works in Digital Forensics Software Corporate Endpoint Triage: How It Works and What to Use seen Sep 2026 · source
-
Corporate Endpoint Triage: How It Works and What to Use
https://belkasoft.com/corporate-endpoint-triagebelka_site_2305 Tue, 08 Sep 2026 00:00:00 GMT How Command-Line Automation Works in Digital Forensics Softwarehttps://belkasoft.com/digital-forensics-command-line-automationbelka_site_2306 Tue, 08 Sep 2026 00:00:00… seen Sep 2026 · source
Custom SQLite artifacts mapping shipped suggested Allows investigators to map tables and columns from unsupported databases to standard artifact fields for search, filter, and review.
Suggested capability: Disk and filesystem forensics. This is our guess, not confirmed.
release
- Introduces custom SQLite artifacts, letting investigators map tables and columns from unsupported databases to standard Belkasoft X artifact fields (timestamps, participant names, message text, identifiers, geolocation) for search, filter, review, and reporting alongside parsed evidence. announced · Sep 2026 · source · release history
Enhanced Android application extraction shipped suggested Improves extraction details for applications including Facebook, Instagram, Telegram, Viber, and WhatsApp.
Suggested capability: Remote forensic collection. This is our guess, not confirmed.
release
- Improves extraction for Android apps including Facebook (contact info, chat threads), Instagram (threads and reactions), Telegram (account owner name, replies, reactions, service messages, call duration), Viber (replies, reactions, call duration, picture captions), WhatsApp (contact merging, reply visualization, vCard… announced · Sep 2026 · source · release history
Event cluster property for System Event Log shipped suggested Groups system log events into activity categories such as system logon/logout, software installation, and remote access.
Suggested capability: Forensic timeline analysis. This is our guess, not confirmed.
release
- Adds Event cluster property to System Event Log artifacts, grouping events into activity categories such as system logon/logout, software installation, remote access, Wi-Fi connections, and system startup/shutdown. announced · Sep 2026 · source · release history
Extended iOS application support shipped suggested Adds support for ChatGPT v1.2026.160 and improves extraction for Apple Unified Logs, Instagram, WeChat, and Zalo.
Suggested capability: Remote forensic collection. This is our guess, not confirmed.
release
- Adds iOS support for ChatGPT v1.2026.160 and improves extraction for Apple Unified Logs (application names in Timeline Info field), Instagram, WeChat (messages, reactions, media), and Zalo (audio artifacts). announced · Sep 2026 · source · release history
New Android application support shipped suggested Adds support for new applications including Burner, FairEmail, Google Play, Google Voice, GroupMe, Life360, Mastodon, MeWe, Microsoft Teams, TeleGuard, Waze, and Wire.
Suggested capability: Disk and filesystem forensics. This is our guess, not confirmed.
release
-
Adds support for new Android applications including Burner, FairEmail, Google Play (
library.db), Google Quick Search Box, Google Voice, GroupMe, Life360, Mastodon, MeWe, Microsoft Teams, TeleGuard, Waze, and Wire. announced · Sep 2026 · source · release history
RSMF 2.0 support shipped Adds support for RSMF 2.0 format and export splitting for large datasets.
release
- Adds RSMF 2.0 support and export splitting for large datasets. announced · Sep 2026 · source · release history
SRUM artifact extraction shipped suggested Extracts and parses System Resource Usage Monitor artifacts, including historical application network activity and timestamps.
Suggested capability: Remote forensic collection. This is our guess, not confirmed.
release
- Adds SRUM (System Resource Usage Monitor) artifact extraction, parsing historical application network activity and associated timestamps. announced · Sep 2026 · source · release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for Belkasoft, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Belkasoft puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Website history
belkasoft.com, every changeBelkasoft's home and pricing pages and 1 more page as they looked each month from August 2021 to October 2026: 15 renders, 5 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Coverage
Missing something? Tell us
What Belkasoft connects to, runs on and detects, read from its release notes and docs. So far: 1 new supported platform.
1 change, tracked since Oct 9, 2026.
-
Oct 92026
new MediaTek chipset physical acquisition support
Covers 23: MT3369, MT6731, MT6737, MT6739, MT6761, MT6762 and 17 more
Belkasoft X currently supports MTK dump acquisition for devices based on the following MediaTek chipsets: MT3369, MT6731, MT6737, MT6739, MT6761, MT6762, MT6763, MT6765, MT6768, MT6769, MT6853, MT6873, MT6877, MT6880, MT6883, MT6885, MT6889, MT6890, MT6893, MT8765, MT8785, MT8766B, MT8768t
Hardware & accelerators 23
Nothing first seen in this window. That doesn't mean Belkasoft shipped nothing, only that we found no record of it.
How we count
Read from 2 of 10 release notes and docs updates we hold for Belkasoft. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through Belkasoft's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
10 entries
No entries match these filters.
- October 20262
- September 20266
- August 20261
- May 20261
Articles
1 article · updated Nov 4, 2026Where Belkasoft turns up in what others publish: how-tos, attack reports that name it, and incident write-ups. A row says why it is here and quotes where the article names it; the link goes to the publisher.
Tutorials & guides 1
-
Forensic Investigation of RAW Images using Belkasoft Evidence Center
In this article, we delve into RAW Image Forensic with Belkasoft , utilizing Belkasoft Evidence Center to conduct a comprehensive forensic investigation of raw disk images.
2 more quotes
Getting Started with Belkasoft Evidence Center Ultimate Firstly , download the Belkasoft Evidence Center ultimate from thi s link .
Exploring Forensic Data with Belkasoft To visualize the cached sites exactly as seen by the user, Click on Cache in Browsers option.
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →