GitLab
GitLab Orbit is GA: Higher agent accuracy, lower token cost (2026-10-29) commercialThe section your link pointed to isn't on GitLab's page any more, so we've brought you to the top.
GitLab is a web-based DevOps platform providing Git repository hosting, CI/CD pipelines, and collaboration tools for software development teams.
glab auth login
glab orbit setup
lang:Dockerfile ^FROM.*php
curl --request POST https://gitlab.com/api/v4/ai/duo_workflows/workflows \
  --header 'PRIVATE-TOKEN: <your_project_access_token>' \
  --header 'Content-Type: application/json' \
  --data '{
    "project_id": 12345,
    "ai_catalog_item_consumer_id": 67,
    "goal": "Class: OpportunityDiscountService\nException: System.NullPointerException\nMessage: Attempt to de-reference a null object\nStack trace: ...\n",
    "start_workflow": true,
    "allow_agent_to_request_user": false,
    "agent_privileges": [1, 2, 3],
    "pre_approved_agent_privileges": [1, 2, 3]
  }'
version: "v1"
environment:
  ambient
components:
  - name: "sf_error_triage"
    type: AgentComponent
    prompt_id: "sf_error_triage_prompt"
    inputs:
      - from: "context:project_id"
        as: "project_id"
      - from: "context:goal"
        as: "error_report"
    toolset:
      - "find_files"
      - "grep"
      - "read_file"
      - "list_commits"
      - "create_issue"
prompts:
  - prompt_id: "sf_error_triage_prompt"
    prompt_template:
      system: |
        You triage errors for a team. Find the source file, read the code,
        list recent commits, and create one issue with root-cause analysis.
      user: |
        Project ID: {{project_id}}
        Error report: {{error_report}}
      placeholder: history
routers:
  - from: "sf_error_triage"
    to: "end"
flow:
  entry_point: "sf_error_triage"
glab govern setup --agents codex,cursor
glab govern doctor
glab govern setup --agents codex,cursor
glab govern doctor
glab govern setup --agents codex,cursor
glab govern doctor
/assign_reviewer @GitLabDuo
/assign_reviewer @GitLabDuo
/assign_reviewer @GitLabDuo
/goal Fix the failing tests in spec/models/user_spec.rb
{
  "gitlab.featureFlags.flowBuilder": true
}
duo run --goal "Fix the checkout timeout. Continue until tests pass and CI is green."
git history drop <commit>
git branch --delete-merged origin
git repack -a -d --filter=blob:limit=1k --drop-filtered
include:
  - project: my-group/my-config
    ref: refs/heads/main
    file: /templates/base.yml
type: AgentComponent
name: "developer_agent"
prompt_id: "developer_agent_prompt"
inputs:
  - from: "context:goal" as: "goal"
  - from: "context:project_id" as: "project_id"
toolset:
  - "read_file"
  - "find_files"
  - "edit_file"
  - "run_command"
  - "create_merge_request"
routers:
  - from: "fix_pipeline_context"
    condition:
      input: "context:fix_pipeline_context.final_answer.decision"
    routes:
      "add_comment": "fix_pipeline_add_comment"
      "create_plan": "fix_pipeline_checkout_existing_branch"
      "direct_code_suggestions": "fix_pipeline_code_suggestions"
      "no_action": "end"
      "default_route": "end"
/goal Fix the failing tests in spec/models/user_spec.rb. Continue until all tests pass locally and CI is green.
/goal Fix the failing tests. Ensure CI is fully green and the fix is reviewed by Duo Developer.
Call the `get_job` MCP tool with:
{
  "job_id": 987654,
  "include": ["log"],
  "byte_offset": 0,
  "byte_limit": 524288
}
Call the `accept_merge_request` MCP tool with:
{
  "merge_request_iid": 42,
  "project_id": 123,
  "strategy": "merge_when_checks_pass"
}
/goal Fix the failing tests in spec/models/user_spec.rb
curl -X POST https://otel-collector.example.com/v1/traces \
  -H "traceparent: $CI_TRACEPARENT" \
  -H "tracestate: $CI_TRACESTATE" \
  -d '{"job": "'$CI_JOB_ID'"}'
build:
  tags:
    - linux-large-amd64
  script:
    - make build
test:
  tags:
    - linux-small-amd64
  script:
    - make test
# .afullhistorycloneoverridepolicy.toml at repo root
schema_version = 2

[policyinfo]
description = "Optimized clone for CI and AI agents"
OptimalForAIAgents = true

[git_config]
"core.compression" = 0
"http.postBuffer" = "1024M"
"pack.threads" = 4

[fetch]
flags = ["--depth=1", "--filter=blob:none"]

[sparse_checkout]
enabled = true
conemode = "auto"
includes = ["/*"]
exclude_extensions = [
  "png", "jpg", "gif", "svg", "pdf",
  "zip", "tar", "gz", "mp4", "exe",
  "dll", "woff", "woff2", "ttf", "psd"
]
case_variants = "both"
./git-clone-override-policy https://example.com/group/my-repo.git
# .afullhistorycloneoverridepolicy.toml at repo root
schema_version = 2

[policyinfo]
description = "Optimized clone for CI and AI agents"
OptimalForAIAgents = true

[git_config]
"core.compression" = 0
"http.postBuffer" = "1024M"
"pack.threads" = 4

[fetch]
flags = ["--depth=1", "--filter=blob:none"]

[sparse_checkout]
enabled = true
conemode = "auto"
includes = ["/*"]
exclude_extensions = [
  "png", "jpg", "gif", "svg", "pdf",
  "zip", "tar", "gz", "mp4", "exe",
  "dll", "woff", "woff2", "ttf", "psd"
]
case_variants = "both"
./git-clone-override-policy https://example.com/group/my-repo.git
glab opentofu state list
AST_ENABLE_MR_PIPELINES: "true"
DAST_FF_XSS_ATTACK: false
/wip
Summary
GitLab is a commercial DevOps and application security platform that covers source control, CI/CD, and vulnerability management in one system, available as SaaSSaaSSoftware delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally. or self-hosted, with a single-tenant GitLab Dedicated option for stricter data residency needs. Its SASTSASTStatic application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment., dependency, and container scanning run inside the same pipelines that build and deploy code, so findings reach a unified vulnerability report rather than a separate dashboard, and it now adds bulk triage features that run false-positive detection and automated fixes across many findings at once. This makes it most relevant to application security and DevSecOps teams who also own the pipeline, rather than SOCSOCA security operations center, the team or function that monitors threats, investigates alerts and coordinates incident response. Its work can be internal, outsourced or shared. analysts working from a separate scanner. Its documentation describes it as an end-to-end workflow spanning planning, code, CI/CD, and monitoring, positioning it as a broader alternative to point tools that handle only scanning or only source control.
GitLab is a web-based DevOps platform providing Git repository hosting, CI/CD pipelines, and collaboration tools for software development teams.
How GitLab helps
Which vulnerability findings in my backlog are actually worth a developer's time?
scans surrounding code for each flagged finding and returns a confidence score with an explanation of whether it is a real risk or a false positive, run across many findings at once instead of one at a time
Can I clear a large SAST backlog without opening every finding by hand?
a bulk-select action in the vulnerability report runs false-positive detection and agentic remediation against a batch of findings, with progress tracking and cancellation, capped by concurrency limits so it doesn't crowd out pipeline builds
Do findings from my other scanners get the same triage treatment as native ones?
imports third-party results in SARIF format into the same vulnerability report, so bulk false-positive detection and remediation apply to findings regardless of which scanner produced them
Will a new Critical or High finding already be triaged by the time I look at it?
pipelines can run false-positive detection and agentic resolution automatically on new Critical and High severity findings, so a confidence score and a fix merge request can exist before a developer opens the finding
Can I keep model inference inside my own cloud boundary instead of sending code to a shared endpoint?
the AI Gateway can run inside a single-tenant deployment against Amazon Bedrock, a Microsoft Foundry endpoint in your Azure tenant, or a model you bring yourself, with per-feature model assignment instead of one global model
Languages
Features
Built from GitLab's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- GitLab covers 3 of the 8 vulnerability assessment methods capabilities we track.
- GitLab covers 1 of the 5 supply chain security capabilities we track.
What GitLab offers you
- CI/CD pipeline integration26
- REST API21
- Command-line interface12
- GraphQL API support12
- Web management console10
- Self-hosted deployment8
- Built-in AI assistant6
- Role-based access control6
- Outbound webhooks (the product notifies you)3
- Scripting API3
- Ticketing integration3
- Administrative audit log2
- Natural-language query2
- User-defined detection rules2
- Agent-based deployment1
- Air-gapped deployment1
- Autonomous investigation and remediation1
- CSV data export1
- Import from a competing product1
- JavaScript scripting support1
- Kubernetes-native deployment1
- ML-based detection1
- Multi-factor authentication1
- SaaS deployment1
- Scheduled jobs1
- Scripting language support1
- SIEM forwarding1
No capabilities match.
Static application security testing 8 features Vulnerability assessment methods since 2015
SAST False Positive Detection shipped Analyzes code surrounding a SAST finding and returns a confidence score and explanation indicating whether the finding represents a real risk or a false positive, runnable manually or automatically on new Critical and High severity findings in pipelines.
Shared capability: Static application security testing
Also counts toward: CI/CD pipeline integration, JavaScript scripting support
release 10 total
-
Backs the analyzer with Anthropic's Claude Mythos 5.1 (a first for any GitLab capability), plus Claude Opus 5.5, Sonnet 5.5, Sonnet 5, and Sonnet 4.6, all running as GitLab-managed models through GitLab's AI gateway.
 Uncover the business logic vulnerabilities SAST scanners miss (2026-10-20) · Oct 2026
· source
· release history
- Enables pipelines to run SAST False Positive Detection and Agentic SAST Vulnerability Resolution automatically on Critical and High severity new findings, so triage and fix MR creation happen before a developer opens the finding. When your backlog outgrows your team, GitLab scales remediation (2026-08-20) · Aug 2026 · source · release history
- SAST False Positive Detection analyzes surrounding code and returns a confidence score and explanation indicating whether a finding is a real risk or a false positive. When your backlog outgrows your team, GitLab scales remediation (2026-08-20) · Aug 2026 · source · release history
- SAST false positive detection is generally available with GitLab Duo Agent Platform, analyzing critical/high vulnerabilities automatically or manually via the vulnerability details page. 18.10 · Mar 2026 · source · release history
- GitLab Duo Security Analyst Agent is generally available to triage vulnerabilities via natural language in Agentic Chat. 18.8 · Jan 2026 · source · release history
- Introduces AI-powered SAST False Positive Detection (Beta) for Critical and High severity vulnerabilities 18.7 · Dec 2025 · source · release history
Advanced SAST customization shipped Allows the creation of custom detection logic and security rules for Static Application Security Testing, tailored to specific organizational requirements.
Shared capability: Static application security testing
Also counts toward: User-defined detection rules, Scripting language support
release 7 total
- Enables Kotlin, Dart, and Scala language support in Advanced SAST with deep taint analysis 19.4 · Sep 2026 · source · release history
- Enables incremental scanning for Advanced SAST to analyze only changed code parts 18.11 · Apr 2026 · source · release history
- C/C++ support in Advanced SAST is generally available with cross-file, cross-function scanning. 18.8 · Jan 2026 · source · release history
- C/C++ support added to Advanced SAST as a beta feature for cross-file and cross-function scanning 18.5 · Oct 2025 · source · release history
- Customizable detection logic for Advanced SAST allows creating custom security rules tailored to organization requirements 18.5 · Oct 2025 · source · release history
-
Adds
PHPsupport to Advanced SAST 18.1 · Jun 2025 · source · release history
Security Review Flow shipped Detects business logic vulnerabilities in merge requests using the Duo Security Review service account.
Shared capability: Static application security testing
release
-
Adds Security Review Flow to check merge request changes for business logic vulnerabilities before they merge.
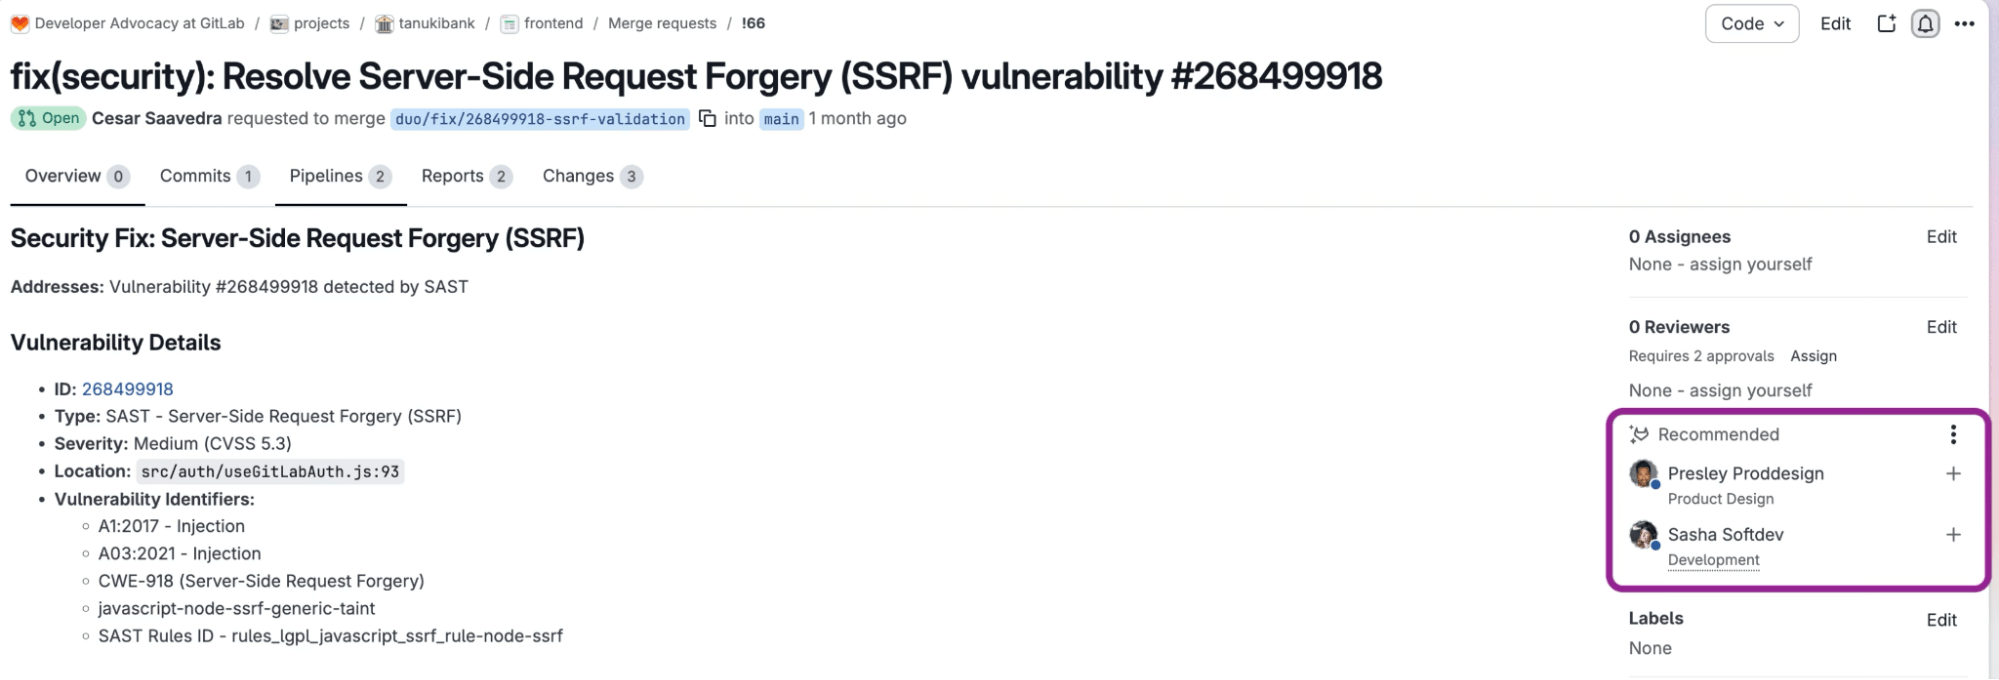 Get every merge request in front of the right reviewer, faster (2026-10-15) · Oct 2026
· source
· release history
-
Supports custom review instructions — covering language conventions, security practices, and path-specific rules — pointing Code Review Flow at a template project so standards travel with the work across a group.
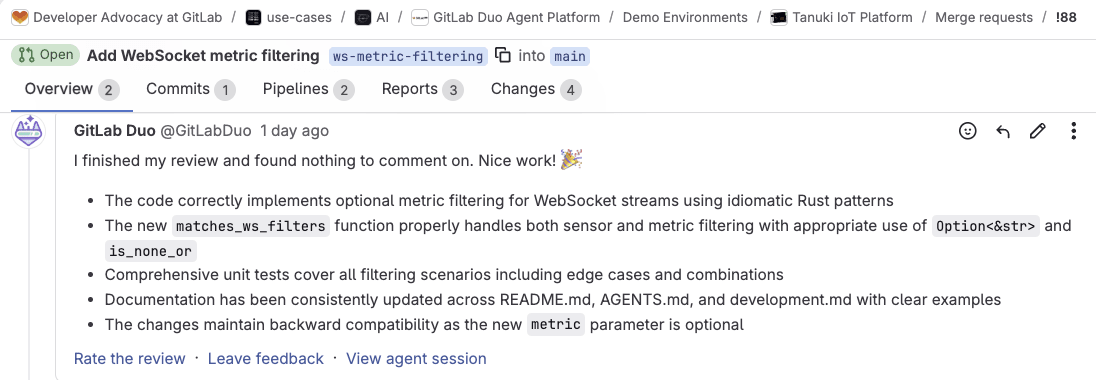 Unblock agentic software delivery with governed code review (2026-10-15) · Oct 2026
· source
· release history
- Adds follow-up review that rechecks prior findings from GitLab Duo Agent Platform, verifies fixes, and carries context forward from the earlier pass. Unblock agentic software delivery with governed code review (2026-10-15) · Oct 2026 · source · release history
- Runs Code Review Flow as a CI/CD job on GitLab-hosted or self-managed runners, integrating agentic review into the same pipeline environment as the rest of delivery. Unblock agentic software delivery with governed code review (2026-10-15) · Oct 2026 · source · release history
- Adds the Security Review Flow feature to detect business logic vulnerabilities in merge requests via the Duo Security Review service account 19.2 · Jul 2026 · source · release history
example
-
Trigger AI-powered code review on a merge request using the new beta capability.
@GitLabDuo17.10 · Mar 2025 · source
Agentic SAST Vulnerability Resolution shipped Automatically creates fix merge requests for SAST findings, triggerable in bulk from the vulnerability report or automatically in pipelines for new Critical and High severity findings.
Shared capability: Static application security testing
Also counts toward: CI/CD pipeline integration
release
- Adds bulk-select UI in the vulnerability report to run SAST False Positive Detection and Agentic SAST Vulnerability Resolution against multiple existing vulnerabilities at once, replacing one-at-a-time manual triage. When your backlog outgrows your team, GitLab scales remediation (2026-08-20) · Aug 2026 · source · release history
- Enables pipelines to run SAST False Positive Detection and Agentic SAST Vulnerability Resolution automatically on Critical and High severity new findings, so triage and fix MR creation happen before a developer opens the finding. When your backlog outgrows your team, GitLab scales remediation (2026-08-20) · Aug 2026 · source · release history
- Adds Dependency scanning auto-remediation (Beta) for automated dependency version bumps and Agentic Breaking Change Resolution 19.2 · Jul 2026 · source · release history
- Adds Agentic SAST Vulnerability Resolution (Beta) to autonomously analyze and fix critical/high SAST findings via merge requests 18.9 · Feb 2026 · source · release history
- Allows per-cache fallback cache keys in CI/CD pipelines, supporting up to 5 keys per job 16.0 · May 2023 · source · release history
- Add button to automatically merge a merge request when the build succeeds 8.3.0 · Dec 2015 · source · release history
SAST analyzer configuration shipped Adds support for specific static analysis engines, such as Semgrep, and configures their availability within the security section.
Shared capability: Static application security testing
release
- Provides a Scanner Enablement Wizard to bulk-apply security profiles and close coverage gaps. 19.1 · Jun 2026 · source · release history
- Dependency Scanning now supports Android projects via the CI/CD Catalog component or template 17.0 · May 2024 · source · release history
- Adds Semgrep-based Scala scanning in SAST, replacing SpotBugs for faster coverage 16.0 · May 2023 · source · release history
- Adds support for the Semgrep static analysis engine on Scala codebases 15.7.0 · Dec 2022 · source · release history
-
Fortify on Demand SAST template available in
project_sast_settings15.3.0 · Aug 2022 · source · release history -
Add
semgrepas a new SAST analyzer. 13.9.0 · Feb 2021 · source · release history
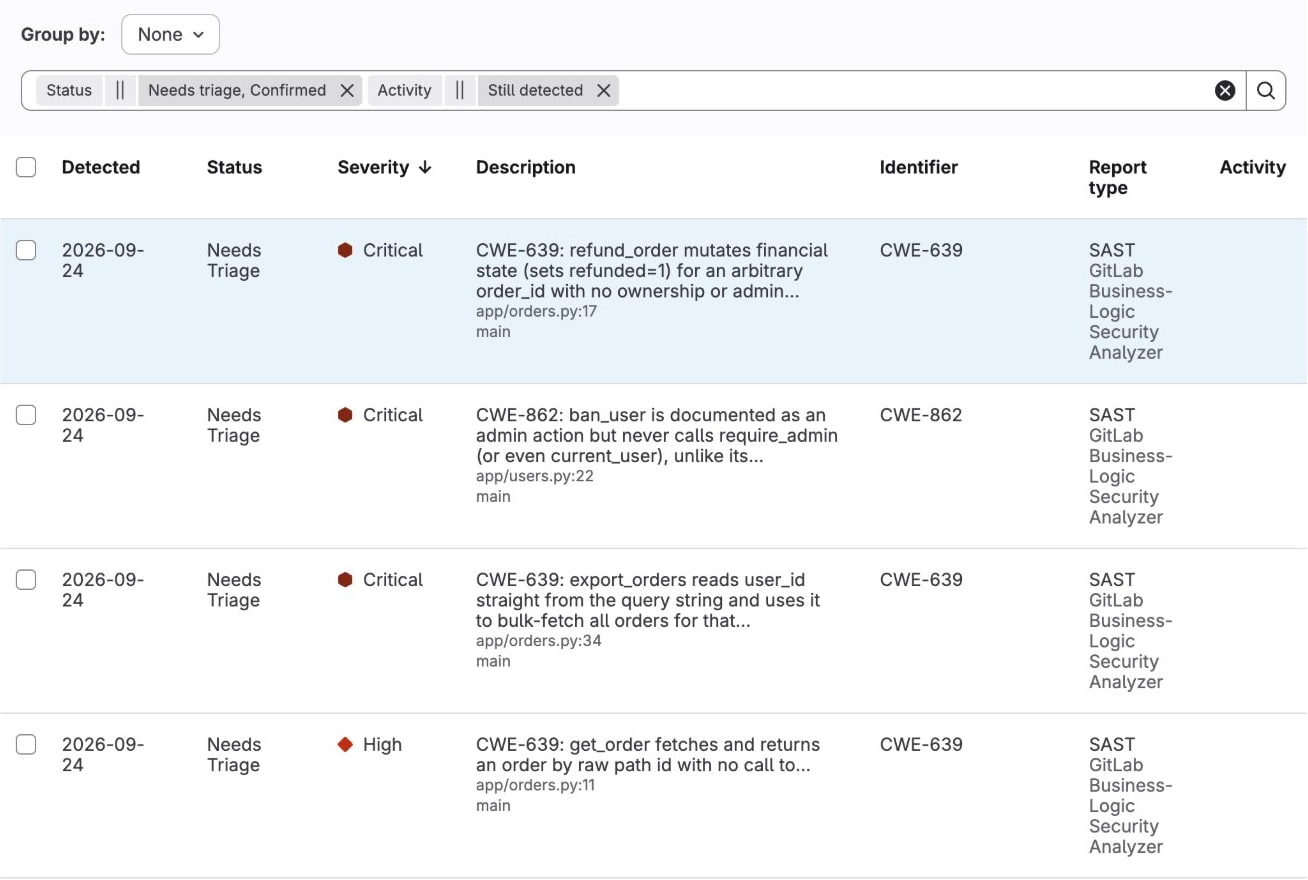
Business Logic Security Analyzer shipped Performs whole-repository SAST scans targeting authorization and mass-assignment vulnerability classes that pattern-based scanners cannot detect, reporting findings as first-class SAST results in the Vulnerability Report and merge request security widget.
Shared capability: Static application security testing
release
- GitLab adds a Business Logic Security Analyzer — powered by Anthropic's Claude Mythos 5.1 — that reads whole repositories and incoming merge requests, infers what each endpoint should enforce, and flags missing authorization checks, broken ownership logic, and business logic flaws that pattern-based scanners… What happens when vulnerabilities are discovered faster than you can fix them? (2026-10-28) · Oct 2026 · source · release history
-
Backs the analyzer with Anthropic's Claude Mythos 5.1 (a first for any GitLab capability), plus Claude Opus 5.5, Sonnet 5.5, Sonnet 5, and Sonnet 4.6, all running as GitLab-managed models through GitLab's AI gateway.
Uncover the business logic vulnerabilities SAST scanners miss (2026-10-20) · Oct 2026
· source
· release history
- Reports findings — including CWE ID, severity (e.g. Critical), and file location — as first-class SAST results in the Vulnerability Report and the merge request security widget. Uncover the business logic vulnerabilities SAST scanners miss (2026-10-20) · Oct 2026 · source · release history
- Adds Business Logic Security Analyzer to GitLab Duo Agent Platform, enabling whole-repository SAST scans targeting broken object-level authorization (CWE-639), missing or improper authorization, and mass assignment — vulnerability classes that pattern-based scanners cannot detect.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Uncover the business logic vulnerabilities SAST scanners miss (2026-10-20) · Oct 2026 · source · release history
-
Available in early access for GitLab Ultimate customers on
GitLab.com; each scan consumes GitLab Credits scaled to the size of the application's attack surface. Uncover the business logic vulnerabilities SAST scanners miss (2026-10-20) · Oct 2026 · source · release history
Bulk agentic SAST triage and remediation shipped A bulk-select UI in the vulnerability report lets users run SAST False Positive Detection and Agentic SAST Vulnerability Resolution against multiple findings at once, with a progress indicator, cancellation control, and concurrency limits to avoid competing with pipeline capacity.
Shared capability: Static application security testing
release
- Adds bulk-select UI in the vulnerability report to run SAST False Positive Detection and Agentic SAST Vulnerability Resolution against multiple existing vulnerabilities at once, replacing one-at-a-time manual triage. When your backlog outgrows your team, GitLab scales remediation (2026-08-20) · Aug 2026 · source · release history
- Enables bulk execution of SAST Vulnerability Resolution and False Positive Analysis flows in the Vulnerability Report 19.3 · Aug 2026 · source · release history
- Adds a progress indicator and cancellation control to bulk agentic jobs, with concurrency limits to prevent bulk runs from competing with pipeline build capacity. When your backlog outgrows your team, GitLab scales remediation (2026-08-20) · Aug 2026 · source · release history
example
-
Triage and remediate your entire SAST backlog at once instead of opening each finding individually.
In the GitLab vulnerability report, select all SAST findings using the bulk-select checkbox, then choose 'Run SAST False Positive Detection' followed by 'Run Agentic SAST Vulnerability Resolution'…When your backlog outgrows your team, GitLab scales remediation (2026-08-20) · Aug 2026 · source
Merge request SAST findings UI shipped Display static analysis scan results directly within the merge request changes view drawer for immediate review.
Shared capability: Static application security testing
Also counts toward: CI/CD pipeline integration
release
- Displays security reports from child pipelines directly in merge request widgets 18.9 · Feb 2026 · source · release history
- Advanced SAST diff-based scanning in merge requests analyzes only code changes to reduce scan times 18.5 · Oct 2025 · source · release history
- Adds Static Analysis Findings display in the Merge request changes view drawer 16.8 · Jan 2024 · source · release history
Web vulnerability scanning 2 features Vulnerability assessment methods since 2020
On-demand DAST scan configuration shipped Provides API controls for dynamic DAST scan execution, including debug logging, AJAX spider usage, and specific scan types during runtime.
Shared capability: Web vulnerability scanning
Also counts toward: REST API
release 8 total
-
Configures API Security Testing with new environment variables:
APISEC_SUCCESS_STATUS_CODES,APISEC_TARGET_CHECK_DISABLED, andAPISEC_TARGET_CHECK_STATUS_CODE. 17.1 · Jun 2024 · source · release history -
Configures Fuzz Testing with new environment variables:
FUZZAPI_SUCCESS_STATUS_CODES,FUZZAPI_TARGET_CHECK_SKIP, andFUZZAPI_TARGET_CHECK_STATUS_CODE. 17.1 · Jun 2024 · source · release history -
Enables GraphQL as a supported scan method for DAST site profiles (
DastSiteProfile) 15.7.0 · Dec 2022 · source · release history -
Add
API_REQUEST_HEADERSenvironment variable to inject custom headers into DAST API scan requests. 15.6.0 · Nov 2022 · source · release history -
Enable
DAST_API_EXCLUDE_URLSenvironment variable to exclude specific URLs from DAST API scans. 15.6.0 · Nov 2022 · source · release history -
add_pre_scan_verification_statusmutation allows admins to set a new pre-scan state for DAST site profiles before execution begins 15.5.0 · Oct 2022 · source · release history
example
-
Configure DAST to exclude reflected XSS checks if they generate too many false positives.
DAST_FF_XSS_ATTACK: false17.11 · Apr 2025 · source
DAST scan configuration storage shipped Provides backend support for storing and managing DAST scan profiles, including branch-specific configurations.
Shared capability: Web vulnerability scanning
release
- Allows filtering project Vulnerability Report by vulnerability identifier (CVE/CWE) with a 20,000 record limit 17.9 · Feb 2025 · source · release history
-
Adds
branch_namefield to DAST profiles for branch-specific scanning configuration. 13.10.0 · Mar 2021 · source · release history -
Add
dast_profilesdatabase table for storing DAST scan configurations. 13.9.0 · Feb 2021 · source · release history
Container image vulnerability scanning 1 feature Vulnerability assessment methods since 2026
Multiple container image scanning shipped Allows passing an array of container images to be scanned simultaneously within CI jobs.
Shared capability: Container image vulnerability scanning
Also counts toward: CI/CD pipeline integration
release
- Multiple Container Scanning allows passing an array of images to be scanned in CI jobs. 18.8 · Jan 2026 · source · release history
Role-based access control 1 feature Identity and access since 2026
Microsoft Foundry integration shipped Enables GitLab Duo to use Microsoft Foundry deployments as a backend for AI inference, supporting Entra identity and Azure RBAC.
Shared capability: Role-based access control
Also counts toward: Role-based access control
release
-
Adds
azure/<deployment-name>as the model identifier format when registering a Microsoft Foundry deployment in GitLab Duo Self-Hosted, allowing GPT, Claude, Llama, and Mistral models to back individual Duo features.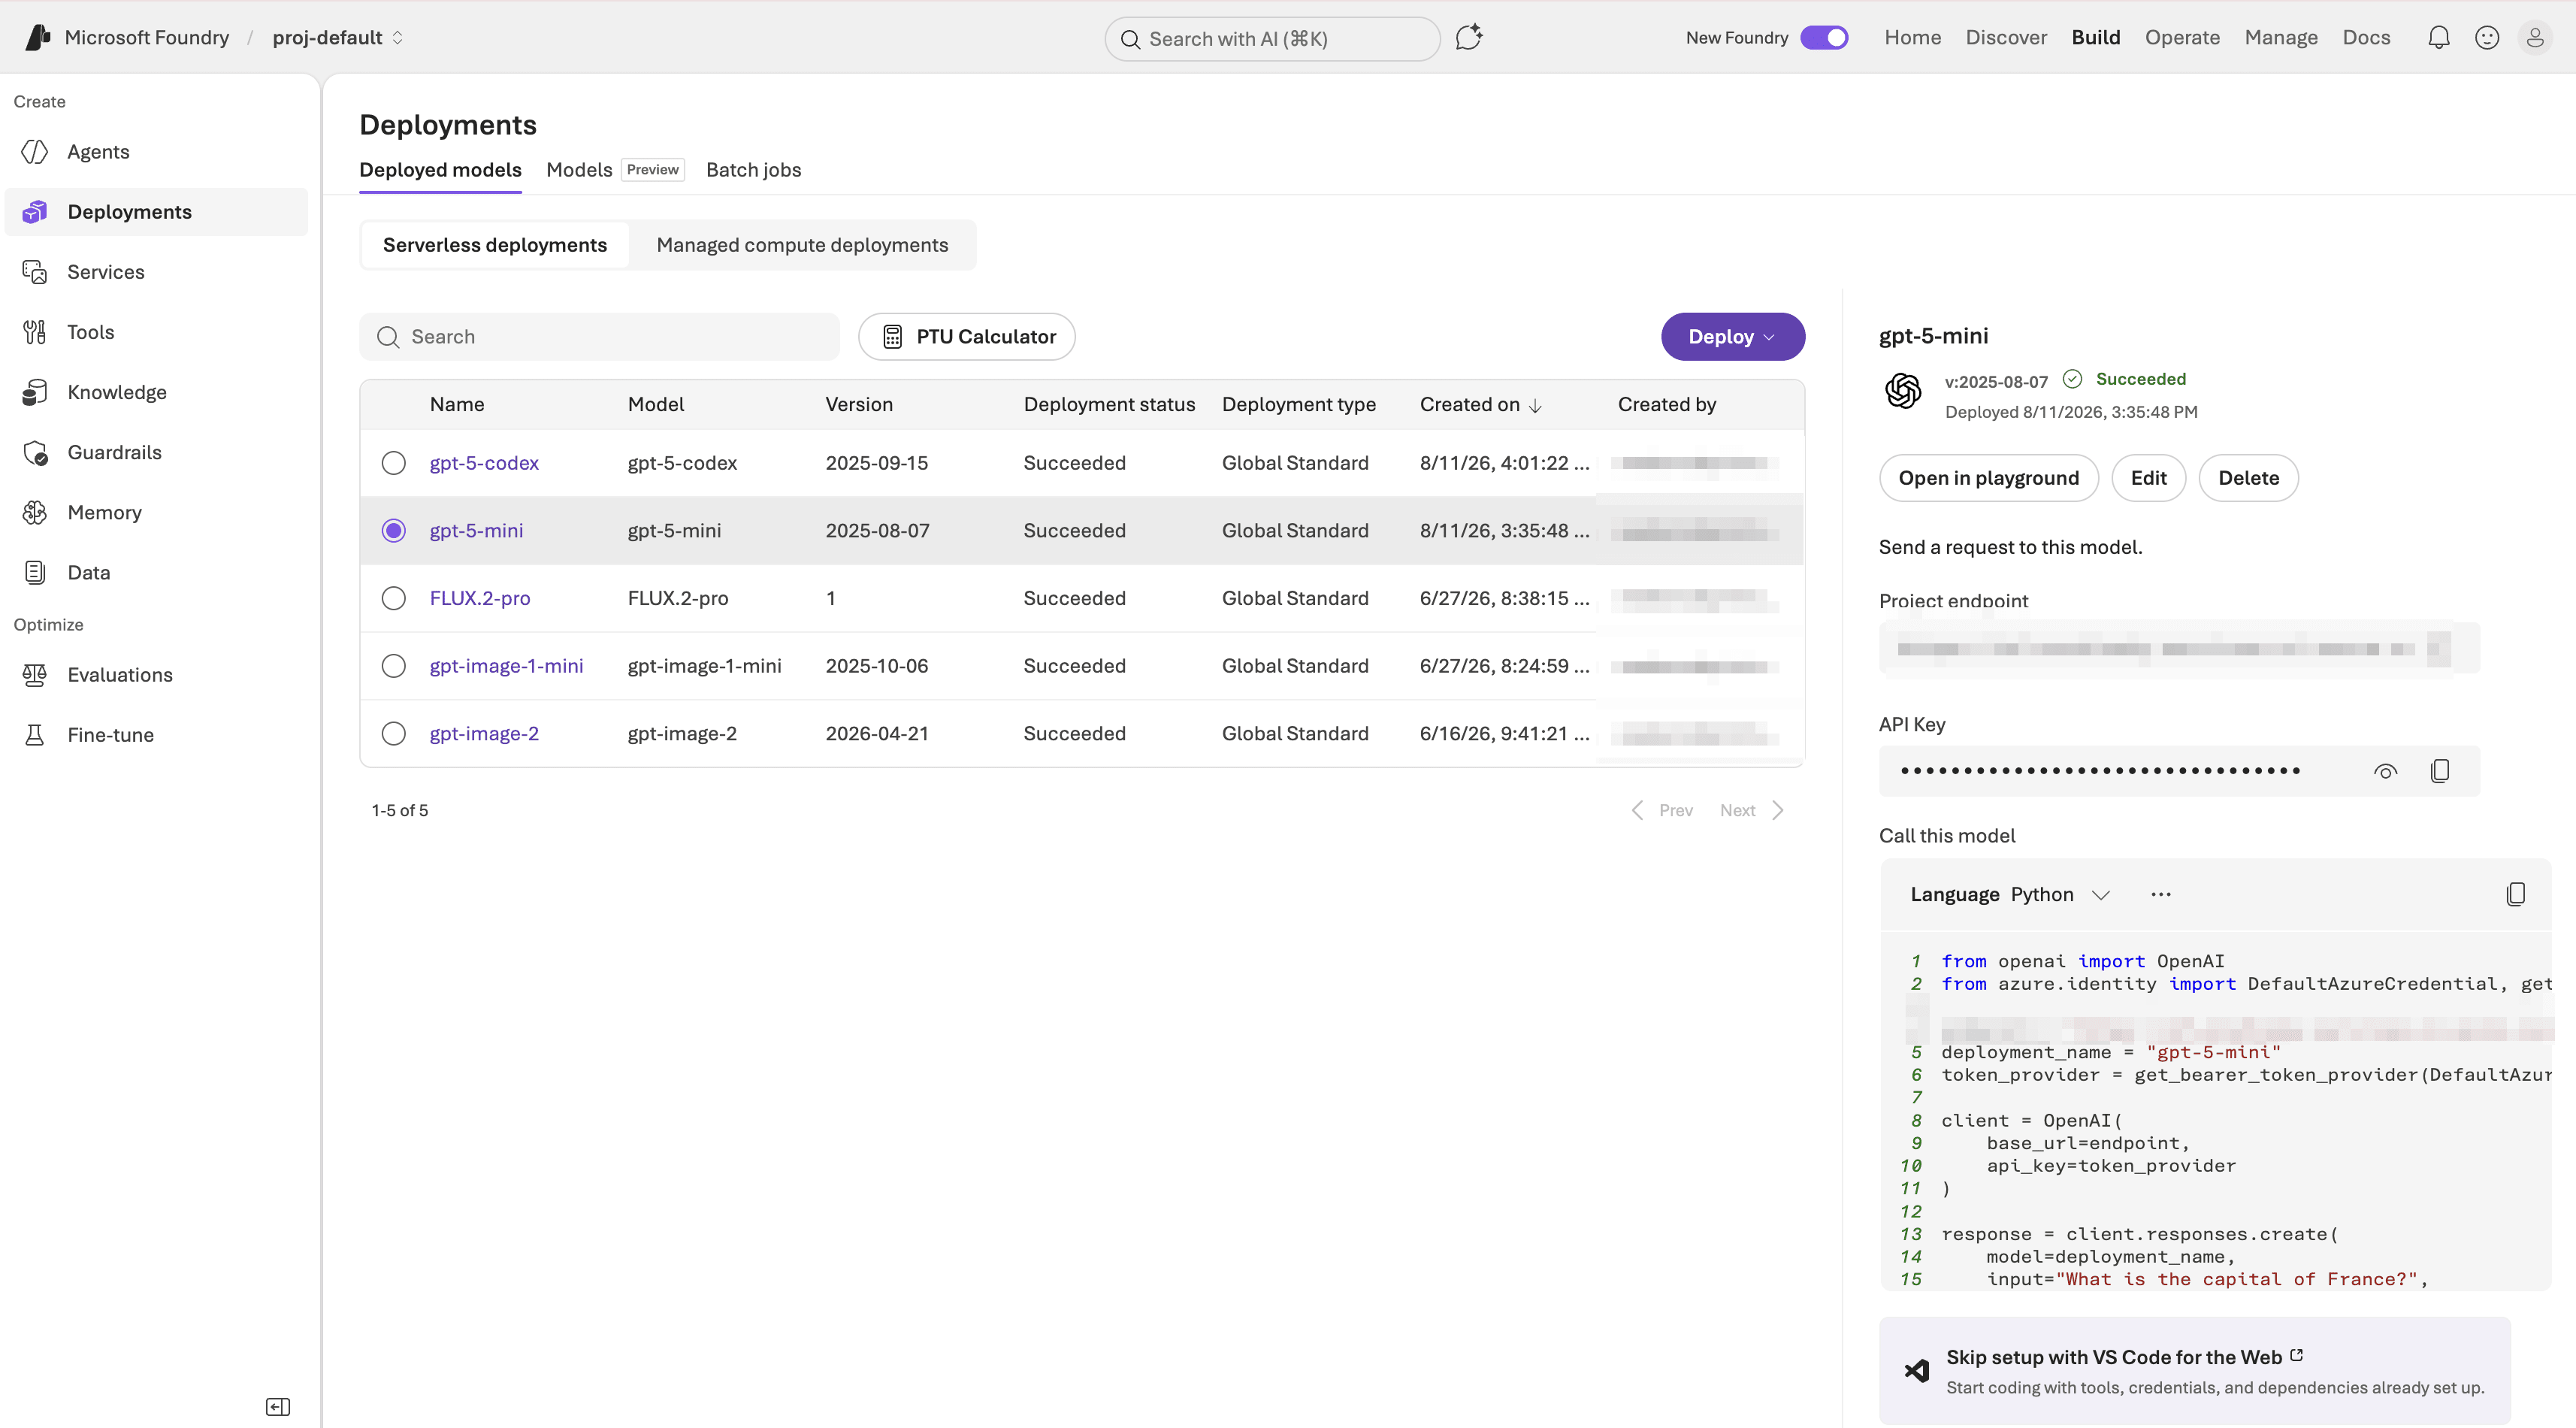 Bring your own model to GitLab Duo Self-Hosted with Microsoft Foundry (2026-09-08) · Sep 2026
· source
· release history
- Adds Microsoft Foundry as a supported backend for the AI Gateway, enabling organizations to serve GitLab Duo inference through Azure-hosted endpoints while keeping inference data within their own Azure tenant. Bring your own model to GitLab Duo Self-Hosted with Microsoft Foundry (2026-09-08) · Sep 2026 · source · release history
- Supports Microsoft Entra identity, Azure RBAC, network isolation, and Azure Policy on Foundry model deployments used with GitLab Duo Self-Hosted. Bring your own model to GitLab Duo Self-Hosted with Microsoft Foundry (2026-09-08) · Sep 2026 · source · release history
- Admin-defined network access controls allow domain denylists/allowlists for Agent Platform remote flows in Settings 19.0 · May 2026 · source · release history
-
Configures network access controls for remote flows using GitLab runners via the
network_policysection inagent-config.yml. 18.10 · Mar 2026 · source · release history
example
-
Register a Microsoft Foundry model deployment for GitLab Duo Agentic Chat, pointing GitLab at the Foundry endpoint with the
azure/identifier prefix.Admin > GitLab Duo > Configure models for GitLab Duo > Add self-hosted model Deployment name: Agentic Chat on Microsoft Foundry Model family: GPT Endpoint:…Bring your own model to GitLab Duo Self-Hosted with Microsoft Foundry (2026-09-08) · Sep 2026 · source
SBOM generation 1 feature Supply chain security since 2022
SBoM tracking support shipped Backend tables and models that track Software Bill of Materials occurrences and sources, enabling SBOM generation workflows.
Shared capability: SBOM generation
release 7 total
- Adds automatic dependency graph generation for Maven and Python SBOM scanning when lock files are missing 18.11 · Apr 2026 · source · release history
-
Supports Dependency Scanning SBOM for Java Gradle
build.gradleandbuild.gradle.ktsfiles with manifest fallback using theDS_ENABLE_MANIFEST_FALLBACKCI/CD variable. 18.10 · Mar 2026 · source · release history - Adds support for license data from CycloneDX SBOMs in License Scanner 17.6 · Nov 2024 · source · release history
- Enables self-hosted large language models for GitLab Duo Code Suggestions by configuring models hosted on-premise or in a private cloud, currently supporting open-source Mistral models on vLLM or AWS Bedrock. 17.5 · Oct 2024 · source · release history
- Integrates dependency scanning SBOM (CycloneDX) data into the dependency graph. 16.11 · Apr 2024 · source · release history
- Adds Prevent pushing and force pushing setting to scan result policies to block direct commits to protected branches 16.6 · Nov 2023 · source · release history
Other / not yet classified 144 features Features we have not matched to a capability yet. A suggested match is marked.
Personal access token visibility shipped Users can view token scopes, assigned roles, expiration dates, usage dates, and the last five distinct connection IP addresses for their personal access tokens.
Also counts toward: REST API
release 38 total
- Adds SCIM token support to the Token Information API Co-Create: Building GitLab with our users (2026-09-10) · Sep 2026 · source · release history
- Adds SCIM token support to the Token Information API, enabling identity and access management systems to inspect SCIM tokens alongside other GitLab tokens. Co-Create: Building GitLab with our users (2026-09-10) · Sep 2026 · source · release history
- Provides the Credentials Inventory API for group owners to programmatically manage Personal Access Tokens, Group Access Tokens, Project Access Tokens, SSH Keys, and GPG Keys. 18.8 · Jan 2026 · source · release history
- Adds service account tokens to the credentials inventory for better visibility into authentication methods across the software supply chain 18.2 · Jul 2025 · source · release history
-
/api/v4/token-informationAPI endpoint for unified identification and revocation of all token types by administrators 17.10 · Mar 2025 · source · release history -
Adds
self_rotatescope for access tokens allowing rotation without a separate request for new token generation 17.9 · Feb 2025 · source · release history
docs
- You can prefill a personal access token’s details by appending the description , and parameters to the URL. For example: The URL must include at least one valid scope. The and description parameters are optional in the URL, but you must enter a token name on the creation form if the URL doesn’t include one. docs update · Sep 2026 · source
- shell shell Personal, group, project, and impersonation access tokens expire at midnight UTC on the expiry date. Expired tokens can no longer be used to authenticate requests and cannot be reactivated. You must create a new token instead. By default, new access tokens must have an expiry date. seen Sep 2026 · source
- the Linux package on each node. Be sure to only add the GitLab SSH in to any of the Patroni nodes on the primary site: are known to work. However, Amazon Aurora is incompatible with load balancing enabled by default from you should select one Praefect node only to run the migrations, AKA the This is an advanced setup. seen Sep 2026 · source
- View token information including scopes, assigned roles, and expiration dates. View usage information including usage dates and the last five distinct connection IP addresses. API. Token usage times are updated every 10 minutes. Token usage IP addresses update every minute. docs update · Aug 2026 · source
Cross-platform binary distribution shipped The override binary runs on Linux, macOS, and Windows for both amd64 and arm64 with no runtime dependency beyond a `git` binary on PATH, covering CMD, PowerShell, Git Bash, and WSL.
Also counts toward: Command-line interface
release 25 total
-
Adds
save_pipelineMCP tool to run, retry, cancel, or rename a CI/CD pipeline.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New MCP tools help platform teams scale automation safely (2026-09-17) · Sep 2026 · source · release history -
Adds the
/goalslash command to GitLab Duo CLI, letting developers describe an outcome and a done-condition in a single prompt; the agent iterates locally until the goal is met or the configured iteration limit is reached, with no turn-by-turn supervision required.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitLab Duo CLI takes a task from goal to done (2026-09-17) · Sep 2026 · source · release history -
Adds
get_jobMCP tool that returns a job by default; passinginclude: ['log']streams the job trace paginated viabyte_offsetandbyte_limit(512 KB per page) so an agent can fetch and diagnose a failed build log directly. New MCP tools help platform teams scale automation (2026-09-17) · Sep 2026 · source · release history -
Adds
save_merge_request_reviewMCP tool covering the full review flow: posting line-level or summary comments, replying in or resolving discussions, submitting a full review, triggering a Duo review, and approving or unapproving. New MCP tools help platform teams scale automation (2026-09-17) · Sep 2026 · source · release history -
Adds
accept_merge_requestMCP tool that merges immediately by default, or waits for checks when passedstrategy: merge_when_checks_pass, or adds to a merge train withadd_to_merge_train_when_checks_pass. New MCP tools help platform teams scale automation (2026-09-17) · Sep 2026 · source · release history -
Adds
get_jobMCP tool that returns a job by default, and withinclude: ["log"]streams the job trace paginated viabyte_offsetandbyte_limit(512 KB per page). New MCP tools help platform teams scale automation safely (2026-09-17) · Sep 2026 · source · release history
example
-
Delegate an open-ended fix to the agent and walk away — it iterates until all tests pass and CI is green, rather than waiting for you to re-prompt each step.
/goal Fix the failing tests in spec/models/user_spec.rb. Continue until all tests pass locally and CI is green.GitLab Duo CLI takes a task from goal to done (2026-09-17) · Sep 2026 · source -
Merge an MR only after all CI checks pass, rather than immediately, to give an agent a safe merge strategy in automated pipelines.
Call the `accept_merge_request` MCP tool with: { "merge_request_iid": 42, "project_id": 123, "strategy": "merge_when_checks_pass" }New MCP tools help platform teams scale automation safely (2026-09-17) · Sep 2026 · source
GitLab Flex credit governance and monitoring shipped Administrators can manage AI usage costs through per-capability controls, flat or per-user caps, and detailed per-event exports for chargeback.
Also counts toward: Web management console
release 20 total
-
Adds
read_agent_artifactscustom role ability to grant dashboard access without requiring Owner role on a top-level group.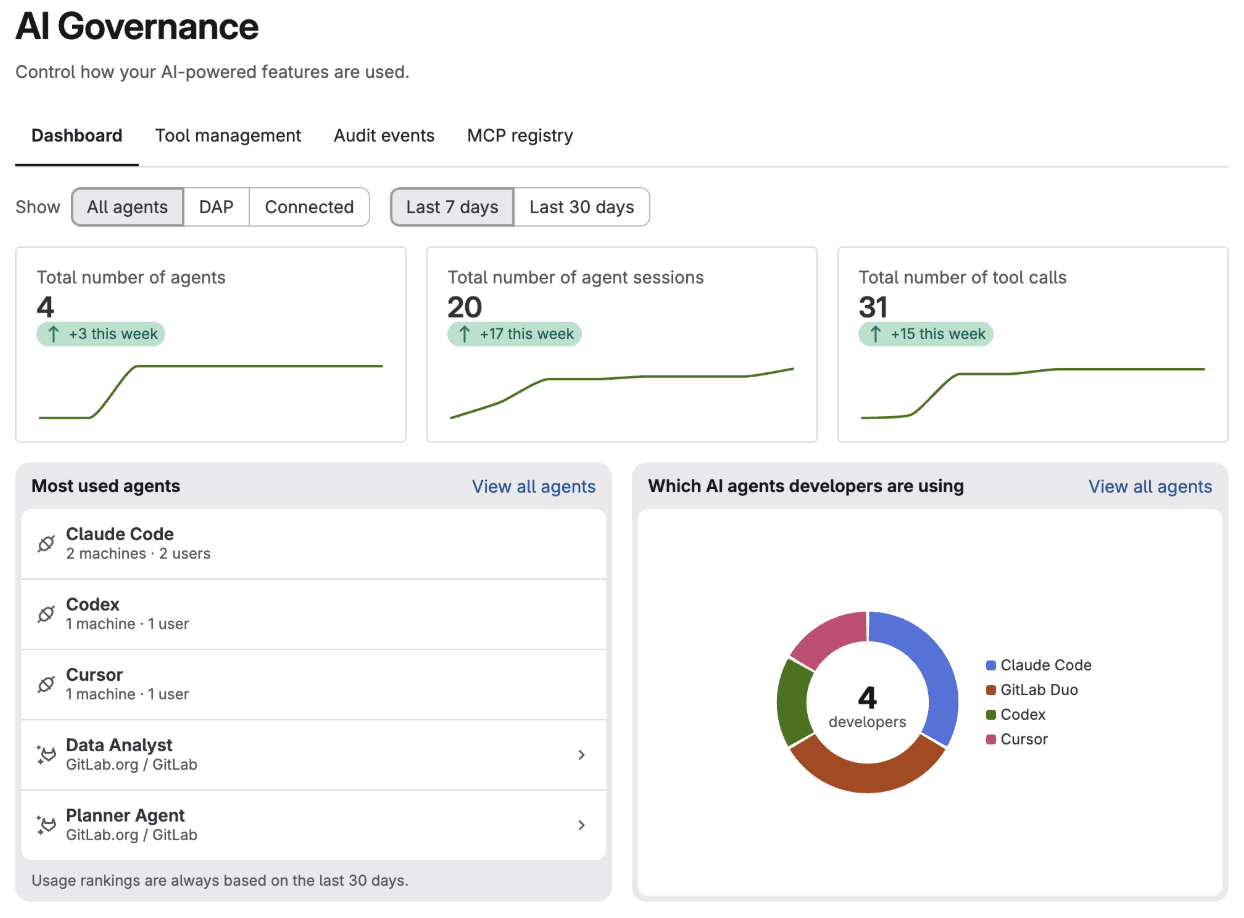 AI Governance: One view of agent activity (2026-10-20) · Oct 2026
· source
· release history
- Enables streaming of agent audit events to a SIEM system and downloading an immutable session copy as evidence from any GitLab Duo Agent Platform session. AI Governance: One view of agent activity (2026-10-20) · Oct 2026 · source · release history
- Argon is available at promotional pricing of 2.86 calls per credit through November 30, 2026, reverting to standard pricing of 1.33 calls per credit on December 1. Gemini 4 Argon on GitLab: Built for long-running agentic work (2026-10-14) · Oct 2026 · source · release history
-
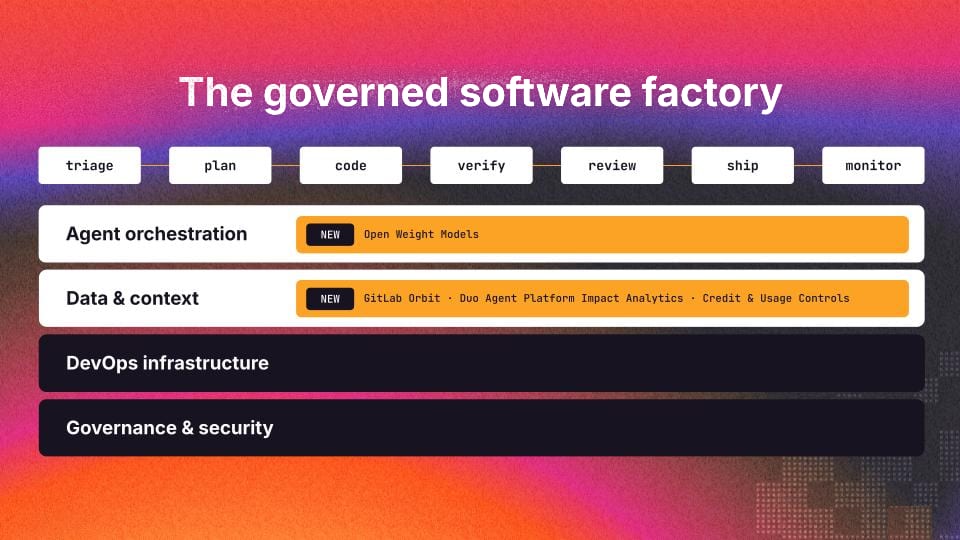
Introduces Duo Agent Platform Impact Analytics, showing credit consumption broken down by team, task, and model for a chosen date range, with open-weight vs. frontier model cost comparison.
 Make every AI credit count: See, cap, and reduce agent spend (2026-10-13) · Oct 2026
· source
· release history
- Introduces the GitLab Credits dashboard, tracing credit usage to the individual user and session level below the team level. Make every AI credit count: See, cap, and reduce agent spend (2026-10-13) · Oct 2026 · source · release history
- Adds credit and usage controls supporting caps at the subscription, group, or user level, with alerts at 50%, 80%, and 100% of spend and automatic pause at the cap; supports per-user flat caps (e.g., 1,000 credits/user/month) and individual overrides (e.g., 500 additional credits). Make every AI credit count: See, cap, and reduce agent spend (2026-10-13) · Oct 2026 · source · release history
example
-
Cap per-user credit spend to prevent runaway agent loops, while giving power users room to experiment without a full escalation.
In your top-level group credit and usage controls, set a flat cap of 1,000 credits per user per month, then apply a 500-credit individual override for engineers running experimental agent sessions.Make every AI credit count: See, cap, and reduce agent spend (2026-10-13) · Oct 2026 · source -
Export granular AI usage data to analyze model costs and token consumption per session.
In the GitLab Credits dashboard, select Export usage data. Wait for email with secure link containing `per-event` file with fields: `Event ID`, `timestamp`, `LLM call count`, `token totals`.See who spent your AI credits and set fair caps per team (2026-09-17) · Sep 2026 · source -
Set a low default AI budget for all developers but override it for a specific researcher doing heavy agentic work.
Go to Admin > GitLab Credits > Credit caps. Set flat cap to `100`. Select Add override, search for user `<researcher_email>`, set cap to `500`, and save.See who spent your AI credits and set fair caps per team (2026-09-17) · Sep 2026 · source
Dependency Firewall shipped A policy-as-code capability that intercepts dependency and artifact fetches, evaluating them against rules for malicious status, vulnerability severity, license type, and package age, with warn and block enforcement modes, an audit dashboard, a CLI pre-check command, a logged bypass mechanism, and policy inheritance from group to project.
Also counts toward: Administrative audit log, CI/CD pipeline integration, Command-line interface, User-defined detection rules, Self-hosted deployment
release 22 total
- GitLab's Dependency Firewall now blocks policy-violating packages before they enter the build, preventing vulnerable or malicious open-source dependencies from reaching production. What happens when vulnerabilities are discovered faster than you can fix them? (2026-10-28) · Oct 2026 · source · release history
-
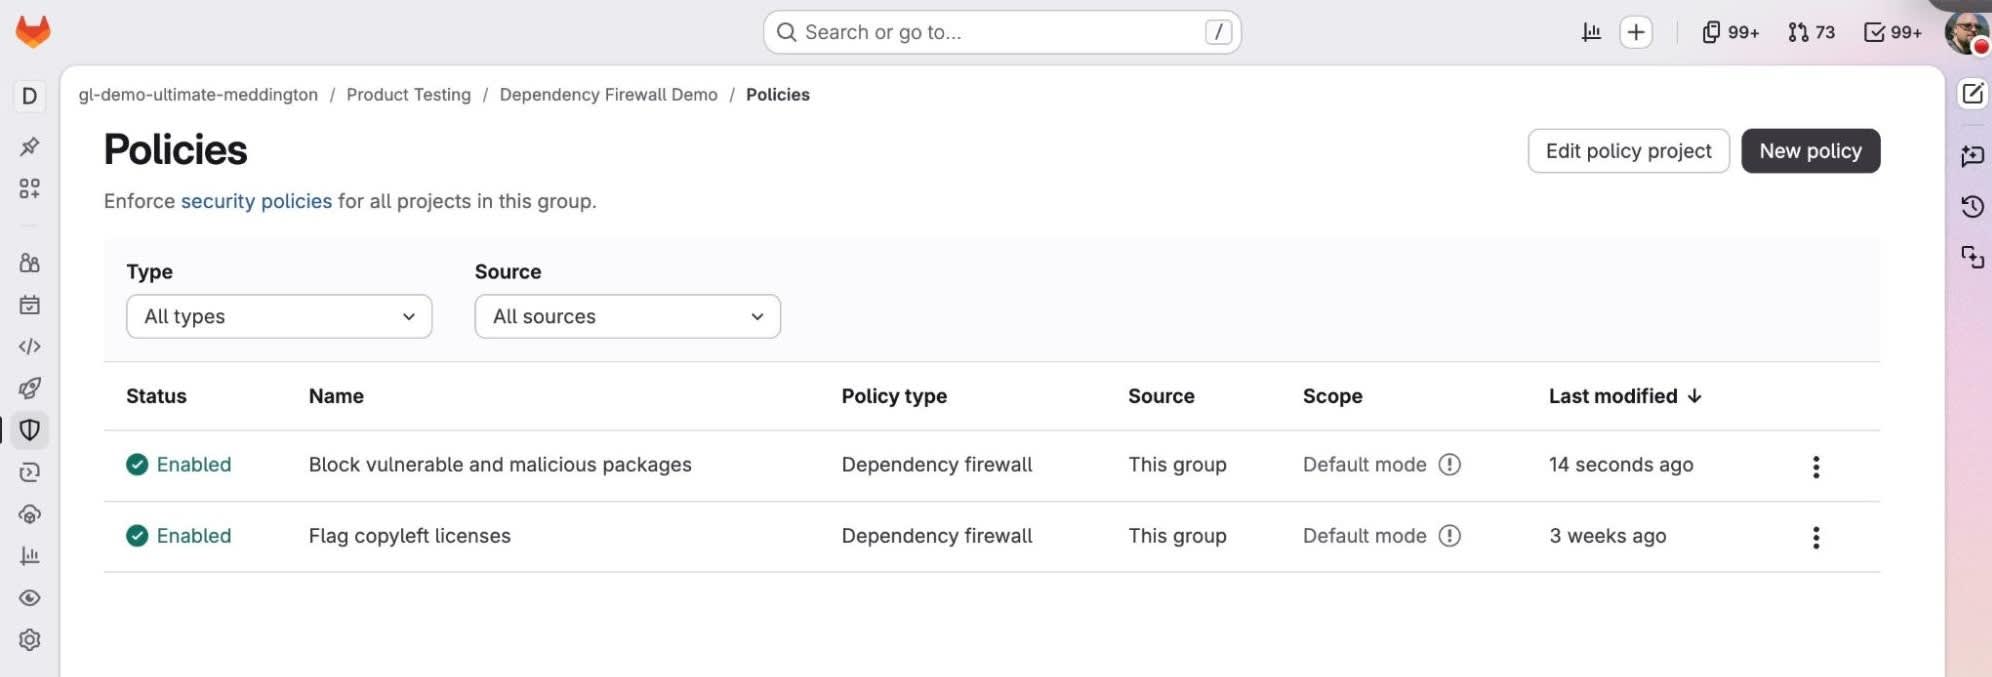
Stores Dependency Firewall rules as code in a security policy project, reviewed and merged like any configuration change, with inheritance from top-level group down to each project and strictest-rule precedence on overlap.
 Dependency Firewall: Block risky packages before the build (2026-10-06) · Oct 2026
· source
· release history
-
New GitLab Dependency Firewall capability is available in early access for
GitLab.comand GitLab Self-Managed customers on Premium or Ultimate tiers. Dependency Firewall: Block risky packages before the build (2026-10-06) · Oct 2026 · source · release history - Adds a GitLab CLI command to check whether a package will pass or be blocked by policy before adding the dependency, covering npm, pip, Poetry, Maven, Gradle, and Bundler. Dependency Firewall: Block risky packages before the build (2026-10-06) · Oct 2026 · source · release history
- Adds a logged bypass mechanism that lets a designated user or token push an approved package through Dependency Firewall on the record. Dependency Firewall: Block risky packages before the build (2026-10-06) · Oct 2026 · source · release history
-
Adds
warnandblockenforcement modes to Dependency Firewall:warnlogs every policy match as an audit event and CI summary line without stopping the build;blockhalts the pipeline and records the reason.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Dependency Firewall: Block risky packages before the build (2026-10-06) · Oct 2026 · source · release history
Flow Creator shipped An agent in Agentic Chat that converts plain-language descriptions into complete, runnable Flow Registry YAML definitions, reading current registry documentation before every response and running a pre-output checklist to catch common schema errors.
Also counts toward: Built-in AI assistant, Natural-language query
release 20 total
-
Custom flows are defined as a single YAML file in
flow registry v1syntax, specifyingAgentComponentagents, toolsets (find_files,grep,read_file,list_commits,create_issue), and prompt templates.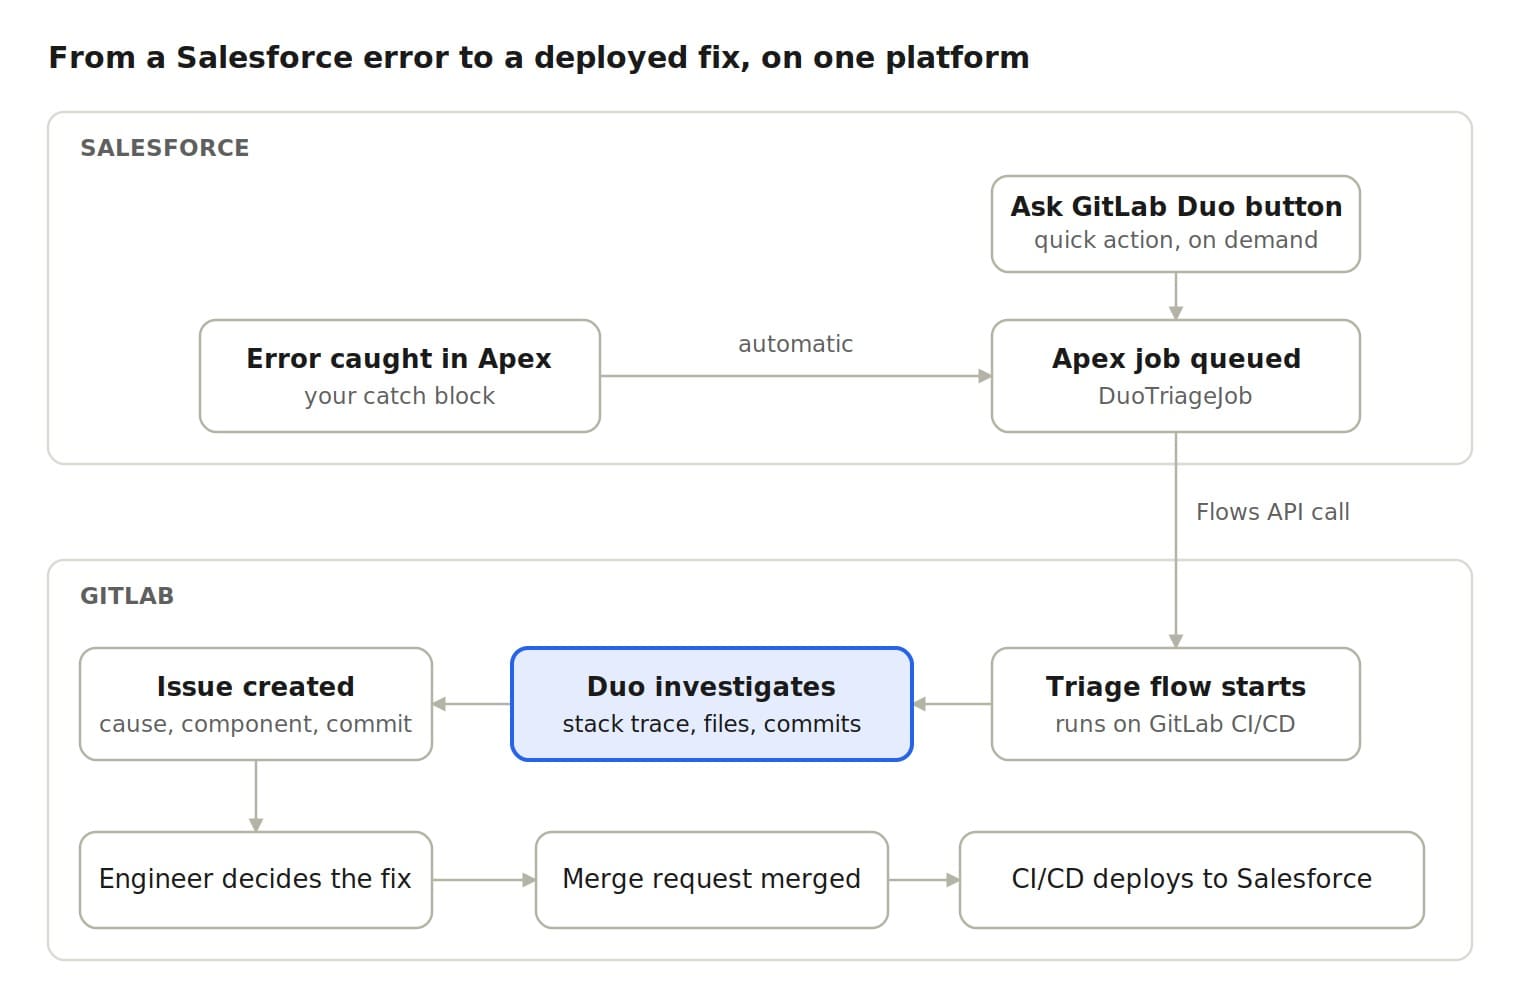 Extend GitLab Duo Agent Platform into your business systems (2026-10-27) · Oct 2026
· source
· release history
- Supports creating and testing custom flows in VS Code with the GitLab flow builder. Extend GitLab Duo Agent Platform into your business systems (2026-10-27) · Oct 2026 · source · release history
-
Adds
save_merge_requestMCP tool to open and update merge requests. New MCP tools help platform teams scale automation safely (2026-09-17) · Sep 2026 · source · release history -
Adds
accept_merge_requestMCP tool that merges immediately by default, waits for checks withstrategy: merge_when_checks_pass, or joins a merge train withadd_to_merge_train_when_checks_pass. New MCP tools help platform teams scale automation safely (2026-09-17) · Sep 2026 · source · release history -
Adds
list_merge_requestsMCP tool supporting group-scope queries. New MCP tools help platform teams scale automation safely (2026-09-17) · Sep 2026 · source · release history -
Adds
list_repository_tree,list_branches,list_tags,list_releases,list_commits,get_commit,add_commit, andfork_repositoryMCP tools for full repository interaction. New MCP tools help platform teams scale automation safely (2026-09-17) · Sep 2026 · source · release history
docs
- Runbooks in GitLab integrate with other GitLab features, like CI/CD pipelines and issues. seen Aug 2026 · source
example
-
Use Flow Creator in Agentic Chat to instantly generate a triage automation without writing any YAML schema.
Steps: 1. Open GitLab Duo Agentic Chat in your GitLab 19.3 instance. 2.Build custom flows in minutes with the Flow Creator agent (2026-08-20) · Aug 2026 · source
Artifact Central shipped An organization-level registry that replaces per-project package and container registries, offering centralized retention rules, storage quotas, access policies, dedicated artifact roles, CI_JOB_TOKEN authentication, hosted/remote/virtual repository types, build provenance attachment, and zero-downtime migration from existing registries.
Also counts toward: CI/CD pipeline integration, Role-based access control
release 21 total
-
Automatically attaches build provenance (pipeline, branch, commit, triggering user) to every artifact published through Artifact Central.
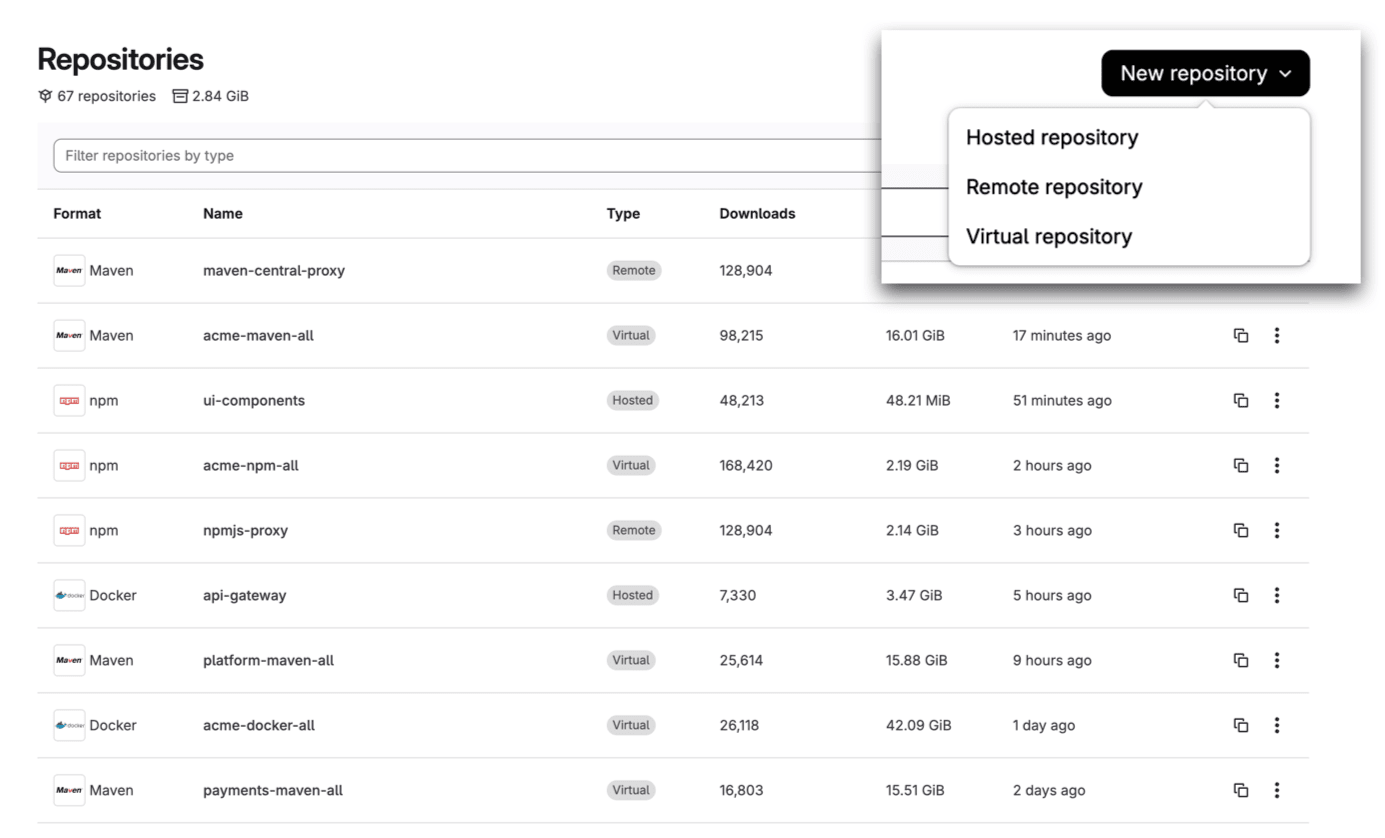 Every artifact your teams ship, assembled right the first time (2026-10-06) · Oct 2026
· source
· release history
-
Supports GitLab Artifact Central and external registries from Sonatype Nexus Repository and JFrog Artifactory without requiring a separate tool deployment.
Dependency Firewall: Block risky packages before the build (2026-10-06) · Oct 2026
· source
· release history
- Supports Maven, npm, Docker, and OCI artifact formats during the beta period. Every artifact your teams ship, assembled right the first time (2026-10-06) · Oct 2026 · source · release history
- Introduces four dedicated artifact roles — Admin, Manager, Contributor, and Viewer — kept separate from existing GitLab project roles so artifact access never affects project privileges. Every artifact your teams ship, assembled right the first time (2026-10-06) · Oct 2026 · source · release history
- Introduces GitLab Artifact Central, an organization-level registry replacing per-project package and container registries, with centralized retention rules, storage quotas, and access policies. Every artifact your teams ship, assembled right the first time (2026-10-06) · Oct 2026 · source · release history
-
Introduces
CI_JOB_TOKENas the authentication mechanism for publishing and pulling artifacts through Artifact Central, eliminating the need for separate service accounts.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Every artifact your teams ship, assembled right the first time (2026-10-06) · Oct 2026 · source · release history
example
-
Add an existing external registry as a Remote repository behind a Virtual repo to start a gradual, zero-downtime migration without bulk-copying data.
In Artifact Central, go to your organization > Artifact Central > Repositories > New Repository, select 'Remote', enter your existing registry URL, then create a 'Virtual' repository that includes…Every artifact your teams ship, assembled right the first time (2026-10-06) · Oct 2026 · source
Agentic work item and vulnerability management shipped Agents can read, update, and resolve vulnerabilities and work items (issues/epics) programmatically.
Also counts toward: Scripting API, Ticketing integration
release 19 total
-
Adds vulnerability tools (
list_vulnerabilities,get_vulnerability,save_vulnerability) to MCP server, available on Ultimate tier. New MCP tools help platform teams scale automation (2026-09-17) · Sep 2026 · source · release history -
Adds
accept_merge_requestMCP tool that merges immediately by default, or waits for checks when passedstrategy: merge_when_checks_pass, or adds to a merge train withadd_to_merge_train_when_checks_pass. New MCP tools help platform teams scale automation (2026-09-17) · Sep 2026 · source · release history -
Adds work item tools to MCP server:
get_work_item,list_work_items,save_work_item, andsave_note(supersedingcreate_merge_request_noteandcreate_workitem_note). New MCP tools help platform teams scale automation (2026-09-17) · Sep 2026 · source · release history -
Adds
save_work_item,list_work_items,get_work_item,save_noteMCP server tools for work item management 19.4 · Sep 2026 · source · release history -
Adds
get_work_item,list_work_items, andsave_work_itemMCP tools covering single-item reads, group/project-scoped search, and create-or-update for any supported work item type (supersedingget_issueandcreate_issue). New MCP tools help platform teams scale automation (2026-09-17) · Sep 2026 · source · release history -
Adds
save_noteMCP tool to comment on a work item or merge request and reply in an existing thread (supersedescreate_merge_request_noteandcreate_workitem_note). New MCP tools help platform teams scale automation (2026-09-17) · Sep 2026 · source · release history
example
-
Define a custom AI triage agent flow that reads repository files and creates a GitLab issue, using flow registry v1 YAML syntax.
version: "v1" environment: ambient components: - name: "sf_error_triage" type: AgentComponent prompt_id: "sf_error_triage_prompt" inputs: - from: "context:project_id" as: "project_id" - from:…
Extend GitLab Duo Agent Platform into your business systems (2026-10-27) · Oct 2026
· source
Repository clone optimization policy shipped A TOML policy file committed to the repository root declaratively configures shallow, partial, and sparse-checkout clone behaviour so that developers, CI jobs, and AI agents automatically get optimized clones without passing flags manually.
release 17 total
- Introduces next-gen SCM architecture with agent-native interfaces that let agents request specific files and history without cloning entire repositories, reducing per-invocation data transfer from 5–10 GB to a fraction of that.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Scaling Git for the agentic software factory (2026-10-13) · Oct 2026 · source · release history
-
Adds
--drop-filteredoption to git-repack(1) to remove locally cached promisor blobs above the given filter threshold, recovering disk space in partial clones. What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history -
Adds
dropsubcommand to git-history(1) to remove a commit and rebase its descendants in a single command:git history drop <commit>.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history -
Adds
.afullhistorycloneoverridepolicy.toml(TOML,schema_version = 2) stored in the repository root to declaratively configure clone optimization policy, including[git_config],[fetch],[sparse_checkout],exclude_extensions,conemode,includes,excludes, andcase_variantsfields.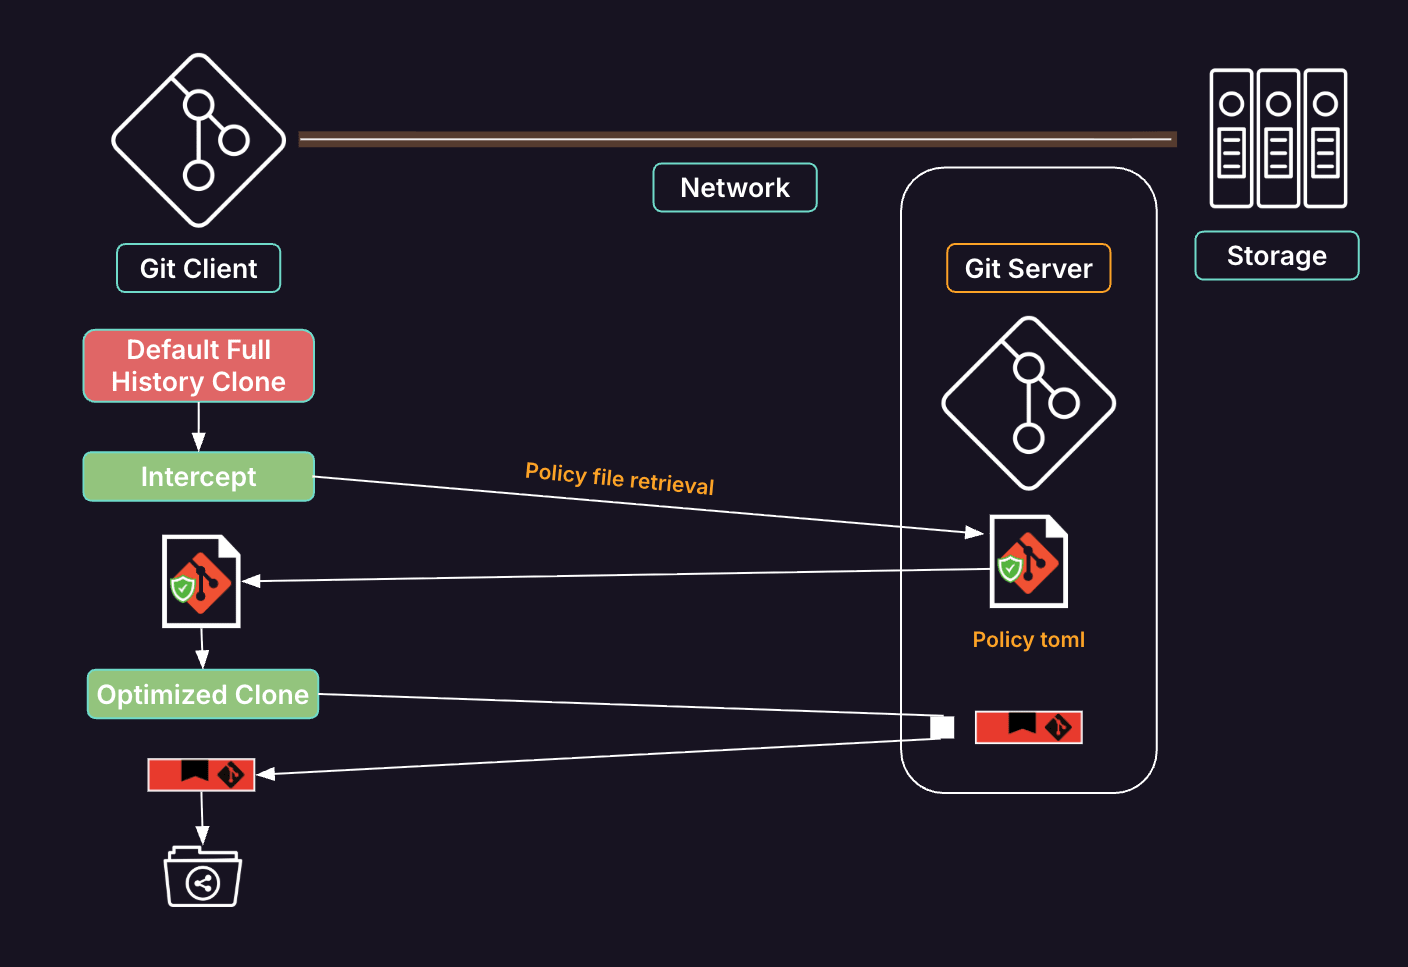 Avoid the massive end-to-end tax of default full history clones (2026-08-18) · Aug 2026
· source
· release history
-
Supports
[fetch]flags such as--depth=1and--filter=blob:nonein policy config to defer blob content and limit history depth on initial clone. Avoid the massive end-to-end tax of default full history clones (2026-08-18) · Aug 2026 · source · release history -
New
[policyinfo]section supports metadata fields such asdescriptionandOptimalForAIAgentsfor auditability and tooling-driven policy generation. Avoid the massive end-to-end tax of default full history clones (2026-08-18) · Aug 2026 · source · release history
example
-
Drop a specific commit from history and automatically rebase its descendants — no interactive rebase editor needed.
git history drop <commit>What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source -
Recover disk space in a blobless partial clone by evicting large cached blobs so Git re-fetches them lazily only when needed.
git repack -a -d --filter=blob:limit=1k --drop-filteredWhat's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source -
Commit a policy file to a monorepo so every bare clone — by developers, CI jobs, or AI agents — automatically gets a shallow partial clone that skips binaries, without anyone remembering the flags.
# .afullhistorycloneoverridepolicy.toml at repo root schema_version = 2 [policyinfo] description = "Optimized clone for CI and AI agents" OptimalForAIAgents = true [git_config] "core.compression" = 0…Avoid the massive end-to-end tax of default full history clones (2026-08-18) · Aug 2026 · source
Agentic pipeline and job interaction shipped Agents can interact with CI/CD pipelines and jobs directly, including running, retrying, cancelling, and retrieving paginated logs for diagnosis.
Also counts toward: CI/CD pipeline integration
release 15 total
- Adds Fix CI/CD Pipeline Flow: select Fix pipeline with Duo from a merge request's Overview or Pipelines tab to have an agent read pipeline logs and propose inline code suggestions, open a new merge request with a fix, or post next-step comments. Three developer tasks worth handing to an agent (2026-10-19) · Oct 2026 · source · release history
-
Adds Fix pipeline with Duo for pipelines not tied to a merge request via
Build > Pipelines, producing a new merge request with the proposed fix. Three developer tasks worth handing to an agent (2026-10-19) · Oct 2026 · source · release history -
Consolidates
get_merge_requestto return commits, diffs, pipelines, conflicts, or notes in a single call, and foldsget_pipeline_jobsintoget_pipeline. Connect your agents to your software lifecycle with the GitLab MCP server (2026-10-15) · Oct 2026 · source · release history -
Adds
get_pipeline(returns a pipeline's status, jobs, downstream pipelines, and artifacts on request),list_pipelines(to surface patterns across recent pipeline runs), andget_artifact_file(to read a single file from a job's artifacts—log, report, or test fixture—without downloading the whole archive) tools. Connect your agents to your software lifecycle with the GitLab MCP server (2026-10-15) · Oct 2026 · source · release history -
Adds
Fix CI/CD Pipeline Flowto diagnose and repair failed CI/CD jobs directly from the merge request.
Get every merge request in front of the right reviewer, faster (2026-10-15) · Oct 2026
· source
· release history
-
Adds
save_pipelineMCP tool to run, retry, cancel, or rename a CI/CD pipeline.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New MCP tools help platform teams scale automation safely (2026-09-17) · Sep 2026 · source · release history
example
-
Send a failing pipeline to the agent for diagnosis and a proposed fix when the pipeline is not attached to a merge request.
In the GitLab UI: Build > Pipelines > [select failing pipeline] > Fix pipeline with DuoThree developer tasks worth handing to an agent (2026-10-19) · Oct 2026 · source -
Trigger a GitLab flow to fix a failing pipeline without leaving the Slack thread where the incident was reported.
@GitLab fix the failing pipeline on the checkout service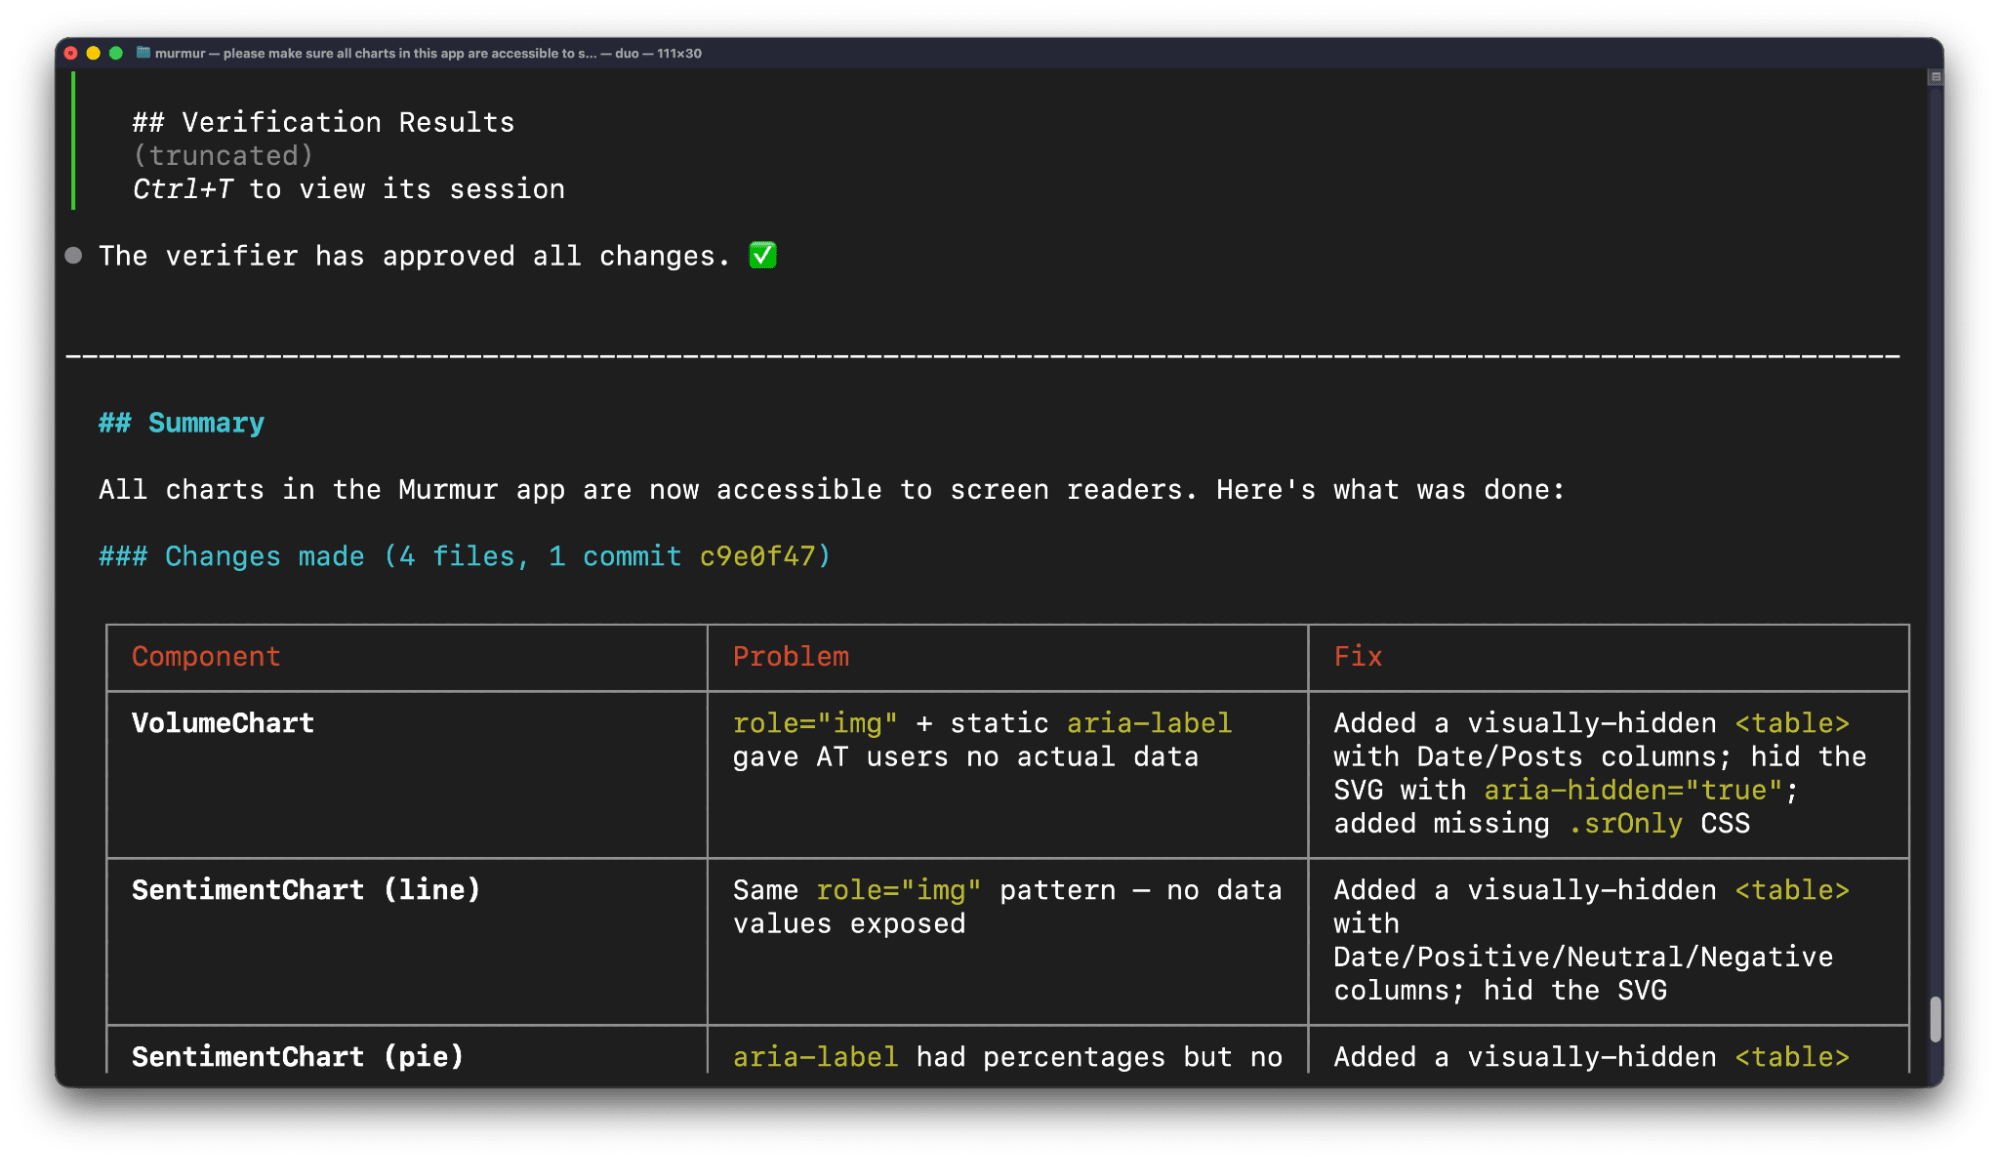 GitLab's agent orchestration eliminates the wait between development stages (2026-10-13) · Oct 2026
· source
-
Delegating the fix of failing tests in a specific file to run until CI is green.
/goal Fix the failing tests in spec/models/user_spec.rb. Continue until all tests pass locally and CI is green.GitLab Duo CLI takes a task from goal to done (2026-09-17) · Sep 2026 · source -
Merge an MR only after all CI checks pass, rather than immediately, to give an agent a safe merge strategy in automated pipelines.
Call the `accept_merge_request` MCP tool with: { "merge_request_iid": 42, "project_id": 123, "strategy": "merge_when_checks_pass" }New MCP tools help platform teams scale automation safely (2026-09-17) · Sep 2026 · source
Lifecycle context graph (GitLab Orbit) shipped Maps code, work items, merge requests, pipelines, deployments, and security findings into a single queryable graph to reduce agent retries and token consumption, and exposes the graph to external agents via MCP.
Also counts toward: CI/CD pipeline integration, REST API
release 17 total
- Enable Orbit on a top-level group to index projects, merge requests, pipelines, work items, security findings, and source code into one relationship graph queryable in plain language.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitLab Orbit: Find vulnerability blast radius without the manual hunt (2026-10-29) · Oct 2026 · source · release history
- External agents such as Claude Code and Codex now reach the Orbit graph over MCP. GitLab Orbit: Find vulnerability blast radius without the manual hunt (2026-10-29) · Oct 2026 · source · release history
-
Orbit is available as query packs (shared pool per org), priced at $30 in GitLab Credits per user per month for 1,000 queries, with overages billed at 33 queries per GitLab Credit (~$0.03 per query).
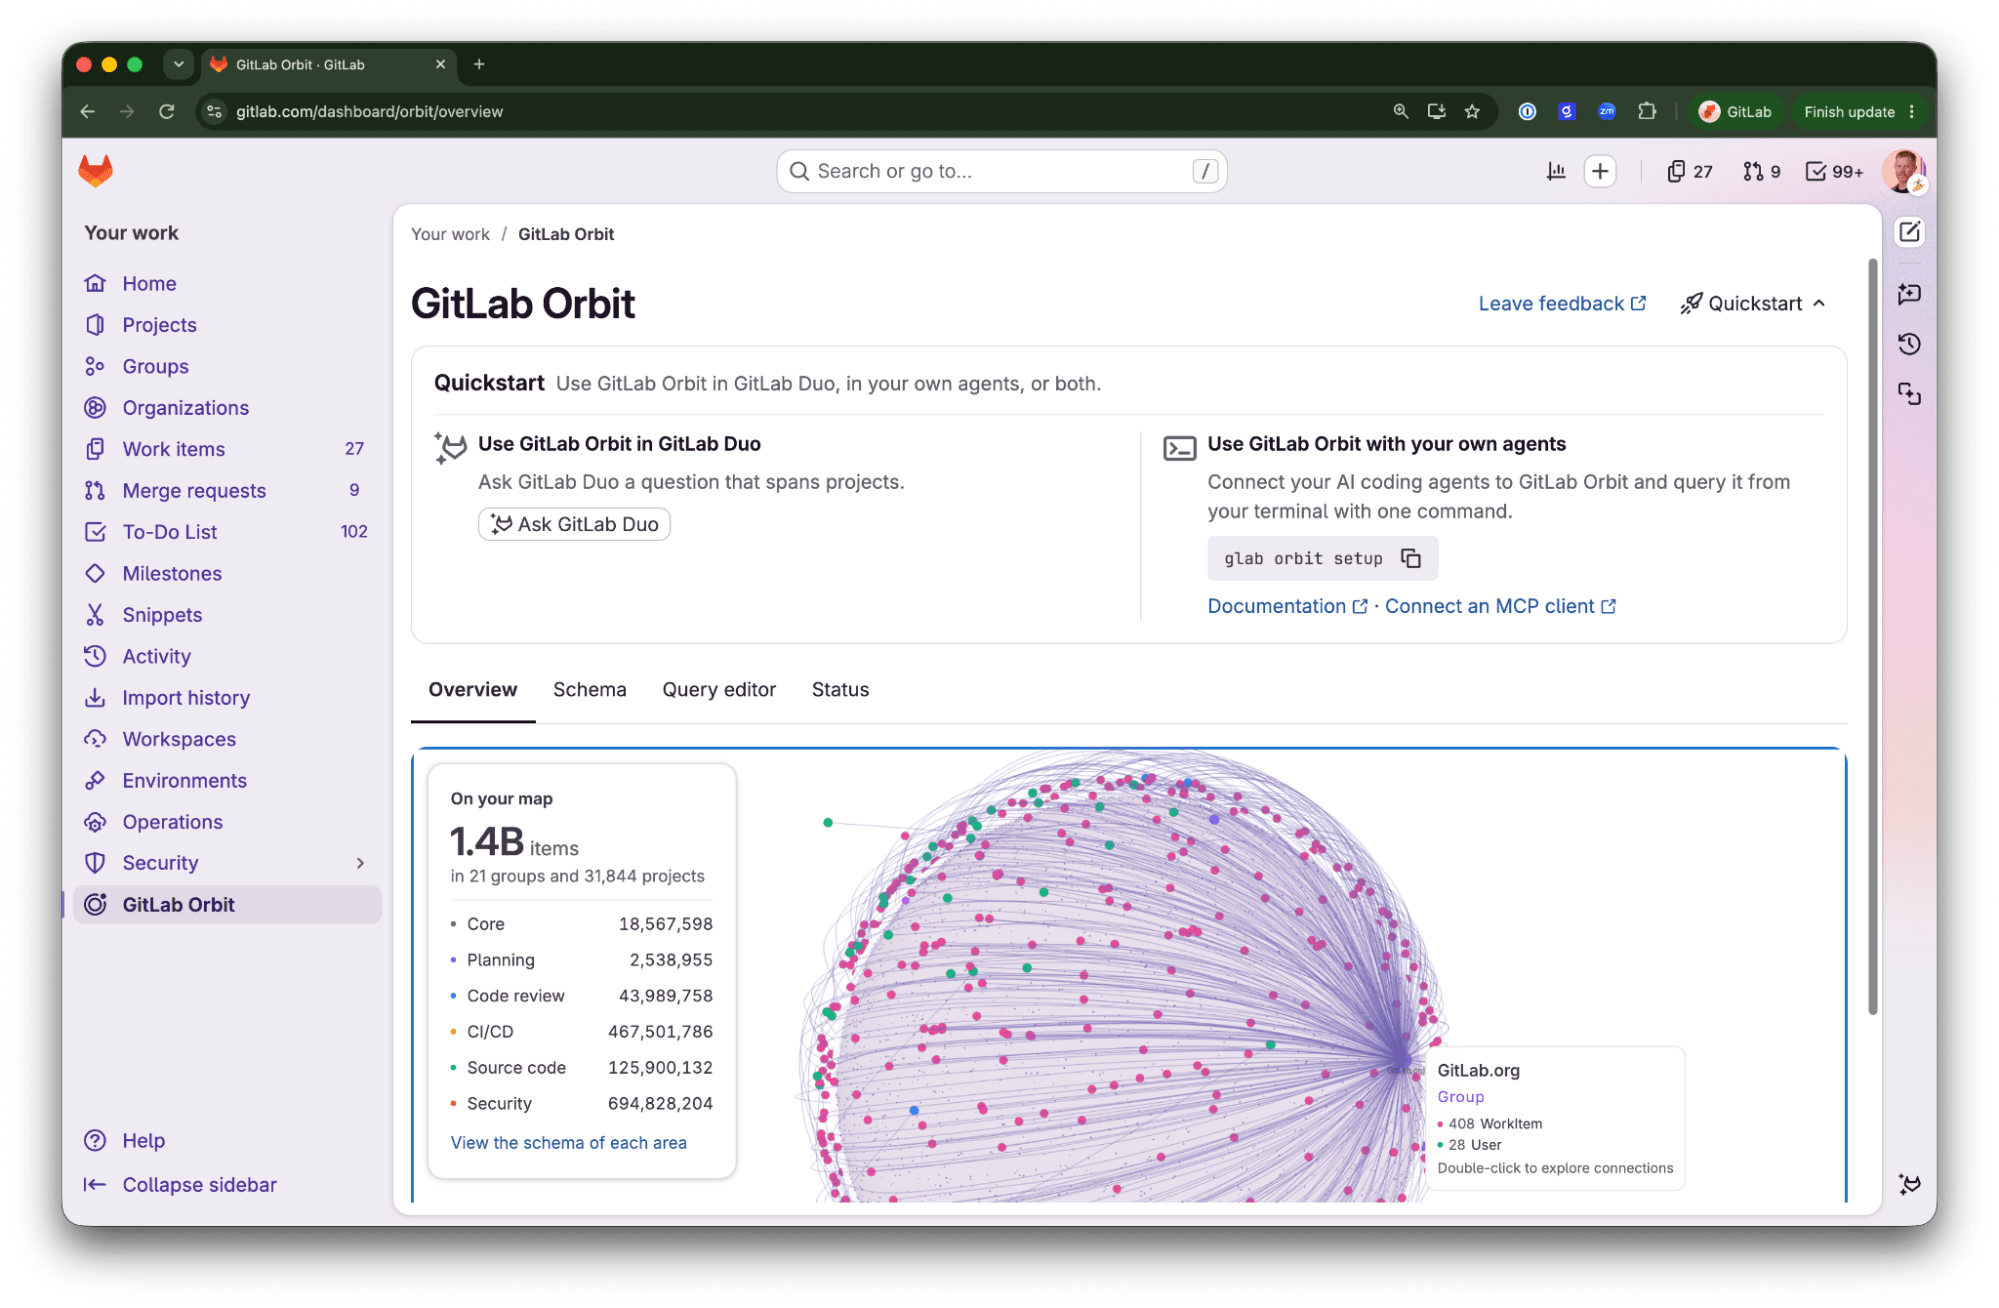 GitLab Orbit is GA: Higher agent accuracy, lower token cost (2026-10-29) · Oct 2026
· source
· release history
- GitLab's built-in Security Analyst Agent now uses Orbit directly to traverse the graph and answer blast-radius questions from indexed project data. GitLab Orbit: Find vulnerability blast radius without the manual hunt (2026-10-29) · Oct 2026 · source · release history
- Engineers query the Orbit graph through the Data Explorer. GitLab Orbit is GA: Higher agent accuracy, lower token cost (2026-10-29) · Oct 2026 · source · release history
- Agents on Duo Agent Platform query Orbit natively with nothing to configure. GitLab Orbit is GA: Higher agent accuracy, lower token cost (2026-10-29) · Oct 2026 · source · release history
example
-
Wire up an MCP-compatible agent such as Claude Code or Cursor to Orbit so it can query live codebase context instead of crawling files.
glab auth login glab orbit setupGitLab Orbit is GA: Higher agent accuracy, lower token cost (2026-10-29) · Oct 2026 · source
Open-ended agentic workflow with auto-completion shipped An agent iterates autonomously on a developer-described outcome until a done-condition is met, without requiring turn-by-turn supervision.
Also counts toward: Autonomous investigation and remediation, CI/CD pipeline integration, Command-line interface, Built-in AI assistant
release 13 total
-
Adds
AI > Sessionsview to follow agent reasoning in real time while Fix CI/CD Pipeline Flow or Agentic Chat runs. Three developer tasks worth handing to an agent (2026-10-19) · Oct 2026 · source · release history -
Enables Allow flow execution and Allow foundational flows under
Settings > GitLab Duo > Change configuration > Flow executionto activate the GitLab Duo Agent Platform for a group.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Three developer tasks worth handing to an agent (2026-10-19) · Oct 2026 · source · release history -
Adds an AI Resource Library of ready-made prompts (e.g.
Summarize Recent Changes to MR/Issue, Debug Failing Pipeline) for use with Agentic Chat. Three developer tasks worth handing to an agent (2026-10-19) · Oct 2026 · source · release history -
Adds
add_branch(to start a feature branch from an agent),get_repository_file(to read a file at any ref without extra API calls),semantic_search(to find code by meaning without knowing the file or symbol name),list_groups(to browse the group hierarchy instead of guessing identifiers), and… Connect your agents to your software lifecycle with the GitLab MCP server (2026-10-15) · Oct 2026 · source · release history -
Adds
list_duo_agents_and_flows(to discover available Duo Agent Platform flows in a project),start_duo_session(to start a GitLab Duo Agent Platform flow from plain-language goals without leaving the MCP client),get_duo_sessionandlist_duo_sessions(to check the progress of running Duo Agent Platform… Connect your agents to your software lifecycle with the GitLab MCP server (2026-10-15) · Oct 2026 · source · release history - Enables isolated agent sessions where unsuccessful experiments can be discarded without disrupting shared code, with successful changes flowing into existing merge requests, pipelines, security checks, and governance controls. Scaling Git for the agentic software factory (2026-10-13) · Oct 2026 · source · release history
example
-
Switch a Duo Agent Platform workflow to Gemini 4 Argon when a task is complex and multi-step — such as an open-ended refactor — where finishing correctly matters more than finishing fast.
In GitLab Duo Agent Platform, open model selection and choose 'Gemini 4 Argon' before delegating your agentic task.Gemini 4 Argon on GitLab: Built for long-running agentic work (2026-10-14) · Oct 2026 · source -
Start a goal-driven flow from the CLI to fix a bug and keep working until CI is green — no manual handoffs between steps.
duo run --goal "Fix the checkout timeout. Continue until tests pass and CI is green."GitLab's agent orchestration eliminates the wait between development stages (2026-10-13) · Oct 2026 · source -
Delegate an open-ended fix to the agent and walk away — it iterates until all tests pass and CI is green, rather than waiting for you to re-prompt each step.
/goal Fix the failing tests in spec/models/user_spec.rb. Continue until all tests pass locally and CI is green.GitLab Duo CLI takes a task from goal to done (2026-09-17) · Sep 2026 · source -
Run the new goal-driven flow from the CLI to automate a task.
/goal Fix the failing tests in spec/models/user_spec.rb19.4 · Sep 2026 · source
Per-feature model assignment shipped Allows administrators to assign specific model deployments to individual Duo features rather than applying a single global model.
Also counts toward: Self-hosted deployment
release 14 total
- Enables model selection between Gemini 4 Argon and Flash models on GitLab Duo Agent Platform, letting teams match each workload to cost and performance needs. Gemini 4 Argon on GitLab: Built for long-running agentic work (2026-10-14) · Oct 2026 · source · release history
-
Adds Model Selection > Manage Models admin setting in top-level group GitLab Duo settings to pin a specific model (e.g.,
GLM 5.3, Kimi K3,MiniMax M3) to each Duo feature, controlling which models team members can use.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Make every AI credit count: See, cap, and reduce agent spend (2026-10-13) · Oct 2026
· source
· release history
- Allows agencies to authorize, restrict, or swap the AI model used for code generation without rebuilding the surrounding governed workflow. GitLab and Claude Code: Fast, compliant AI (2026-09-29) · Sep 2026 · source · release history
-
The new per-event export file surfaces Event ID,
timestamp,event type,product and flow type,session identifier, User ID, Namespace ID, Project ID,credits consumed(quantity and unit), LLM call count,token totals,models used, Flex capability, andsubscription name— enabling per-team…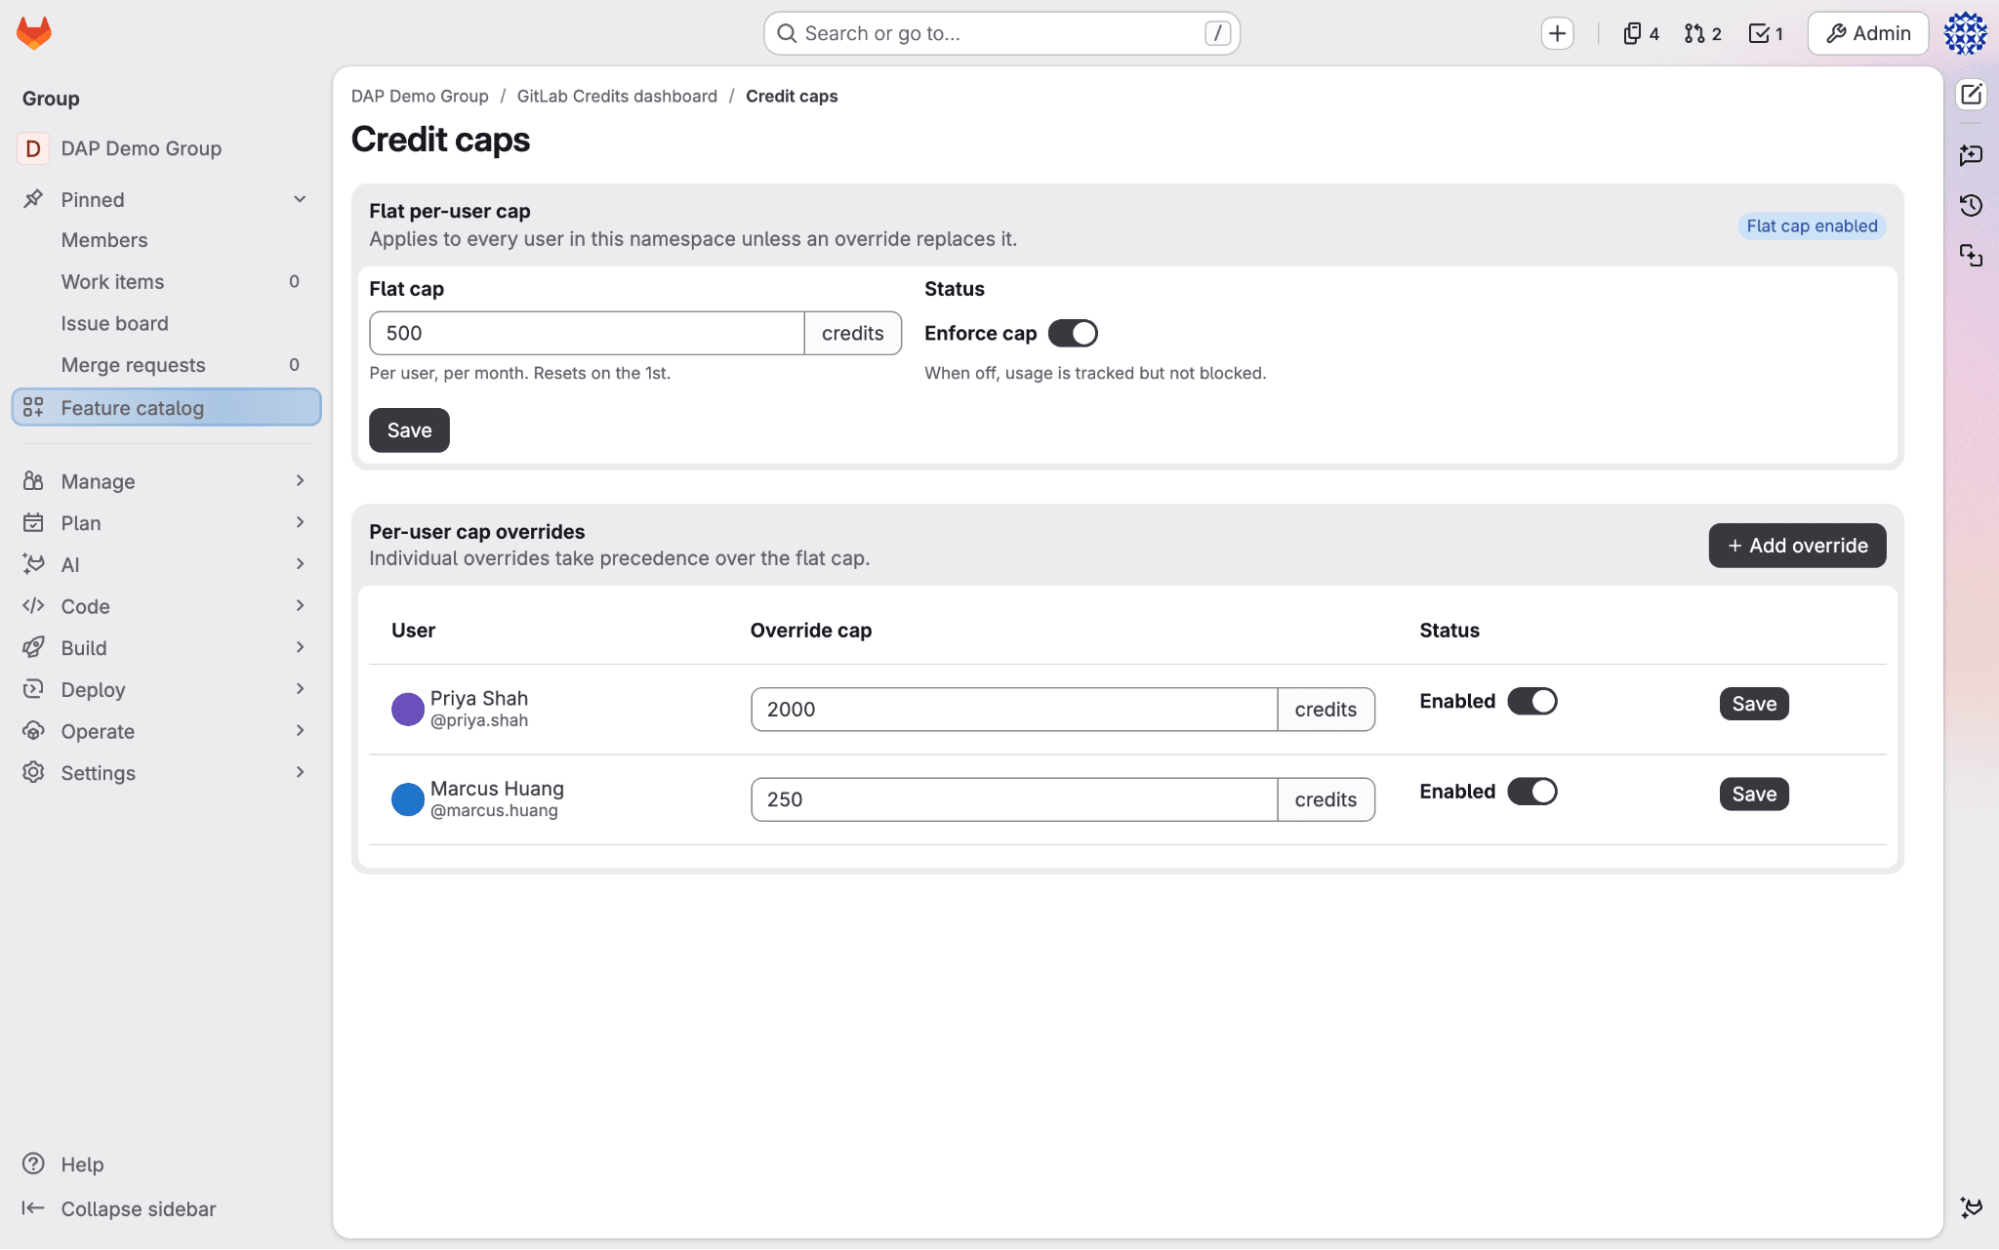 See who spent your AI credits and set fair caps per team (2026-09-17) · Sep 2026
· source
· release history
-
Adds
get_project,list_projects,list_project_members, andget_userMCP tools for project and user lookups. New MCP tools help platform teams scale automation safely (2026-09-17) · Sep 2026 · source · release history -
Adds a per-developer
GitLab Creditsview under User settings showing a daily consumption chart with product filter and date range controls, scoped to the individual user's own events. See who spent your AI credits and set fair caps per team (2026-09-17) · Sep 2026 · source · release history
example
-
Switch a Duo Agent Platform workflow to Gemini 4 Argon when a task is complex and multi-step — such as an open-ended refactor — where finishing correctly matters more than finishing fast.
In GitLab Duo Agent Platform, open model selection and choose 'Gemini 4 Argon' before delegating your agentic task.Gemini 4 Argon on GitLab: Built for long-running agentic work (2026-10-14) · Oct 2026 · source -
Pin a cheaper open-weight model to a high-frequency routine workload to avoid defaulting every agent run to an expensive frontier model.
In your top-level group, go to Settings > GitLab Duo > Model Selection > Manage Models, then pin `Kimi K3` to Agentic Chat and `MiniMax M3` to agents and flows.Make every AI credit count: See, cap, and reduce agent spend (2026-10-13) · Oct 2026 · source -
Pull a per-event export to identify which user and session drove last week's credit spike, then map namespaces to finance cost centers for automatic chargeback.
From the GitLab Credits dashboard (or GitLab Flex month overview), select 'Export usage data'. Choose a date range up to 31 days.See who spent your AI credits and set fair caps per team (2026-09-17) · Sep 2026 · source
Compliance framework management shipped Allows configuring and managing compliance frameworks, including out-of-the-box standards and custom requirements mapped to external controls.
release 17 total
- Generally available the Security Manager role for granular security feature access. 19.1 · Jun 2026 · source · release history
- Adds 19 compliance framework templates (ISO 27001:2022, SOC 2, etc.) for the Compliance center. 19.1 · Jun 2026 · source · release history
- Betas the Security Manager role for focused vulnerability management and compliance access 18.11 · Apr 2026 · source · release history
- Changes compliance framework controls to show scan success/failure based solely on scan completion rather than overall pipeline status 18.7 · Dec 2025 · source · release history
- Compliance framework controls now show scan success/failure based solely on scan completion, which may differ from the previous reliance on overall pipeline status. 18.7 · Dec 2025 · source · release history
- Instance-wide compliance and security policy groups enable centralized management of frameworks and policies across all top-level groups on Self-Managed/Dedicated instances 18.5 · Oct 2025 · source · release history
Duo Agent Platform on Dedicated shipped Deploys the AI Gateway and full Duo Agent Platform capabilities — including automated code review, pipeline fix, and security analysis — inside a GitLab Dedicated single-tenant AWS environment, keeping AI inference within the customer's chosen region and data residency boundary.
Also counts toward: CI/CD pipeline integration
release 14 total
-
Enables
GitLab Duo Agent Platform Self-Hosteddeployment on agency-controlled infrastructure, supporting air-gapped networks, data residency mandates, and policies barring code transmission to third-party APIs.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitLab and Claude Code: Fast, compliant AI (2026-09-29) · Sep 2026 · source · release history - Supports running AI models on GPU-enabled virtual machines in a private cloud for self-managed inference without dedicated hardware costs. GitLab and Claude Code: Fast, compliant AI (2026-09-29) · Sep 2026 · source · release history
- Runner fleet creation and management is self-serviceable through Switchboard, the GitLab Dedicated management console. Scale software delivery pipelines in isolation without owning the runner fleet (2026-08-25) · Aug 2026 · source · release history
- Enables secure connectivity to internal artifact registries, secret managers, and deploy targets via AWS PrivateLink. Scale software delivery pipelines in isolation without owning the runner fleet (2026-08-25) · Aug 2026 · source · release history
- Backs the offering with a 99.9% uptime SLA and highly available, autoscaling runner architecture to handle bursty CI workloads. Scale software delivery pipelines in isolation without owning the runner fleet (2026-08-25) · Aug 2026 · source · release history
- Each CI job runs in a newly provisioned, short-lived VM deleted after completion, enforcing job-level process isolation. Scale software delivery pipelines in isolation without owning the runner fleet (2026-08-25) · Aug 2026 · source · release history
Cluster monitoring and management shipped Provides an open source cluster health dashboard and supports managing multiple Kubernetes clusters from the core UI.
Also counts toward: Web management console
release 14 total
- Adds support for Kubernetes 1.36 19.3 · Aug 2026 · source · release history
- Adds support for Kubernetes 1.35 18.11 · Apr 2026 · source · release history
- Adds support for Kubernetes version 1.32. 17.11 · Apr 2025 · source · release history
-
Adds
--helm-release-valuesand--helm-release-values-fromflags toglab cluster agent bootstrapfor custom Helm values 17.6 · Nov 2024 · source · release history -
Introduces
glab cluster agent bootstrapCLI command to simplify installing the Kubernetes agent on top of an existing Flux installation. 17.5 · Oct 2024 · source · release history - Allows GitLab to initiate the connection to the Kubernetes cluster for the agent, enabling use behind firewalled GitLab installations where the cluster cannot reach GitLab directly. 17.5 · Oct 2024 · source · release history
Custom Flows automation triggers shipped Flows can be triggered automatically by events, such as opening a merge request.
Also counts toward: Web management console, Outbound webhooks (the product notifies you)
release 12 total
-
Enables lookup of a flow's
ai_catalog_item_consumer_idvia GraphQL query, required to invoke a specific custom flow through the Flows API.
Extend GitLab Duo Agent Platform into your business systems (2026-10-27) · Oct 2026
· source
· release history
-
Introduces the
POST /api/v4/ai/duo_workflows/workflowsFlows API endpoint (generally available from GitLab 19.5) to trigger custom AI agent flows from any external system via HTTP.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Extend GitLab Duo Agent Platform into your business systems (2026-10-27) · Oct 2026 · source · release history -
Supports Custom Flows to compose Recommend Reviewers Flow alongside other agentic workflows your team already runs.
Get every merge request in front of the right reviewer, faster (2026-10-15) · Oct 2026
· source
· release history
-
Adds Custom Flows to chain agents into multi-step sequences triggered by GitLab events (mention, assignment, or pipeline) and run them in CI/CD pipelines, including human-in-the-loop checkpoints.
GitLab's agent orchestration eliminates the wait between development stages (2026-10-13) · Oct 2026
· source
· release history
-
Adds
@GitLabmention support in Slack channels and threads via GitLab for Slack, letting teams trigger flows (e.g. fix a failing pipeline, create an issue) directly from a conversation. GitLab's agent orchestration eliminates the wait between development stages (2026-10-13) · Oct 2026 · source · release history - Adds Created trigger action for Merge requests in AI > Triggers 19.4 · Sep 2026 · source · release history
example
-
Trigger a custom Duo Agent flow from any external system to auto-triage an error and open a GitLab issue — no human required.
curl --request POST https://gitlab.com/api/v4/ai/duo_workflows/workflows \ --header 'PRIVATE-TOKEN: <your_project_access_token>' \ --header 'Content-Type: application/json' \ --data '{ "project_id":…Extend GitLab Duo Agent Platform into your business systems (2026-10-27) · Oct 2026 · source
Agentic merge request workflow automation shipped Agents can perform the full MR lifecycle, including reviews, approvals, and safe merging strategies based on CI status.
release 10 total
- Agent output from Argon-powered runs lands in a merge request for team review with full change context. Gemini 4 Argon on GitLab: Built for long-running agentic work (2026-10-14) · Oct 2026 · source · release history
- Provides a governed merge request gate that enforces review, scans, and approvals on every change regardless of which AI model or coding tool generated it. GitLab and Claude Code: Fast, compliant AI (2026-09-29) · Sep 2026 · source · release history
-
Adds
save_merge_requesttool to open and update merge requests via the GitLab MCP server. New MCP tools help platform teams scale automation (2026-09-17) · Sep 2026 · source · release history -
Adds
save_merge_request_reviewMCP tool covering the full review flow: posting line-level or summary comments, replying in or resolving discussions, submitting a full review, triggering a Duo review, and approving or unapproving. New MCP tools help platform teams scale automation (2026-09-17) · Sep 2026 · source · release history -
Adds
accept_merge_requesttool with default immediate merge orstrategy: merge_when_checks_pass/add_to_merge_train_when_checks_passoptions. New MCP tools help platform teams scale automation (2026-09-17) · Sep 2026 · source · release history -
Adds
save_merge_request_reviewtool covering line-level comments, discussion replies/resolutions, full review submission, Duo triggers, and approve/unapprove actions. New MCP tools help platform teams scale automation (2026-09-17) · Sep 2026 · source · release history
example
-
Toggle the Work In Progress status of a merge request via CLI to hide it from review boards.
/wip8.13.0 · Oct 2016 · source
Instance-level streaming audit events shipped Allows instance administrators to stream audit events in real-time from the entire instance for monitoring and compliance.
release 11 total
- Allows administrators to toggle audit streams as active or inactive via the UI to temporarily deactivate streaming to destinations like AWS and GCP 18.2 · Jul 2025 · source · release history
- Adds filter functionality for all audit streaming destinations including by event type, groups, and projects through the UI 18.2 · Jul 2025 · source · release history
- Generates User authorized an OAuth application audit events when users authorize OAuth applications 17.9 · Feb 2025 · source · release history
-
Adds
merge_request_mergedaudit event type with detailed merge information 17.6 · Nov 2024 · source · release history - Adds authentication log for tracking CI/CD job token authentications, downloadable as CSV 17.6 · Nov 2024 · source · release history
- Adds Instance-level audit event streaming destination to AWS S3 16.8 · Jan 2024 · source · release history
Custom Flows governance shipped Enabling a generated flow requires the Maintainer role or higher; Group Owners and instance administrators can disable Custom Flows entirely, and every flow runs under a scoped service account with composite identity bounded to the top-level group.
Also counts toward: Role-based access control
release 9 total
-
Supports
allow_agent_to_request_user,agent_privileges, andpre_approved_agent_privilegesrequest body fields to control autonomous flow execution and tool permissions without human intervention.
Extend GitLab Duo Agent Platform into your business systems (2026-10-27) · Oct 2026
· source
· release history
- New AI > Flows > New flow UI path in a GitLab project allows creating, enabling, and managing custom agent flows, including an Enable action scoped to a specific project under the Managed tab. Extend GitLab Duo Agent Platform into your business systems (2026-10-27) · Oct 2026 · source · release history
- Enabling a generated flow still requires the Maintainer role or higher; Group Owners and instance administrators can disable Custom Flows entirely. Every flow runs under a scoped service account with composite identity, bounded to the top-level group. Build custom flows in minutes with the Flow Creator agent (2026-08-20) · Aug 2026 · source · release history
- Adds tool-level approval policies (Allow, Ask, Deny) for GitLab Duo agents. 19.1 · Jun 2026 · source · release history
- AI Catalog can be confined to a group hierarchy to block external agents not owned by the group 19.0 · May 2026 · source · release history
- Allows reporting of agents and flows to instance administrators via an abuse report mechanism 18.7 · Dec 2025 · source · release history
example
-
Enable a custom flow and retrieve its
ai_catalog_item_consumer_idfor use in API calls, then navigate to AI > Flows in your project.1. In your GitLab project, go to AI > Flows. 2. Open the 'Managed' tab and select your flow. 3. Select 'Enable' and choose the project that holds your source code. 4.Extend GitLab Duo Agent Platform into your business systems (2026-10-27) · Oct 2026 · source
SARIF import for unified vulnerability report shipped Third-party scanner findings in SARIF format can be imported into the unified vulnerability report, making bulk agentic triage and remediation flows available to findings from any external scanner.
release 10 total
- Ingests third-party scanner output in SARIF format, rolling those findings into the same risk score, charts, and per-project view alongside native GitLab scanner results. Track organization-wide security risk in one dashboard (2026-10-08) · Oct 2026 · source · release history
- Supports importing third-party scanner findings in SARIF format into the unified vulnerability report, making bulk agentic flows available to findings from any external scanner. When your backlog outgrows your team, GitLab scales remediation (2026-08-20) · Aug 2026 · source · release history
- Enables importing findings from any SARIF 2.1.0-compliant scanner into GitLab vulnerability management. 19.1 · Jun 2026 · source · release history
-
DS_FF_LINK_COMPONENTS_TO_GIT_FILES=trueenvironment variable enables linking dependency scanning results to source files 18.3 · Aug 2025 · source · release history - Corpus management is enabled for self-managed installs to handle vulnerability data lifecycle 14.8.0 · Feb 2022 · source · release history
- Bring SAST to Core: bandit, Flawfinder, Gitleaks, Gosec, Kubesec, NodeJsScan, phpcs-security-audit, PMD, Security Code Scan, Sobelow, SpotBugs are now core detections 13.3.0 · Aug 2020 · source · release history
Terraform state integration shipped Enables managing Terraform state files directly within the tool with API support and CI_JOB_TOKEN authentication.
Also counts toward: REST API
release 9 total
- Completes the REST API for Terraform state protection rules (create, read, update, delete) Co-Create: Building GitLab with our users (2026-09-10) · Sep 2026 · source · release history
-
glab opentofu state unlocksubcommand added to GitLab CLI for unlocking managed state 18.3 · Aug 2025 · source · release history -
glab opentofu state deletesubcommand added to GitLab CLI for deleting entire or versioned state 18.3 · Aug 2025 · source · release history -
glab opentofu state listsubcommand added to GitLab CLI for managing managed state backends 18.3 · Aug 2025 · source · release history -
glab opentofu state downloadsubcommand added to GitLab CLI for downloading specific state versions 18.3 · Aug 2025 · source · release history -
glab opentofu state locksubcommand added to GitLab CLI for locking managed state 18.3 · Aug 2025 · source · release history
example
-
List all OpenTofu state versions managed by GitLab for a specific project.
glab opentofu state list18.3 · Aug 2025 · source
Vulnerability report filters and metadata shipped Enhances vulnerability reports with granular scanner/report type filters, EPSS/KEV/CVSS data fields, and CVE/CWE filtering.
release 10 total
- Displays CVSS 4.0 scores in the UI, vulnerability reports, and API queries 18.11 · Apr 2026 · source · release history
- Adds filtering by vulnerability identifier, reachability value, and policy violation bypass reason to the vulnerability report 18.7 · Dec 2025 · source · release history
- Adds grouping data by OWASP 2021 categories to the vulnerability report 18.7 · Dec 2025 · source · release history
- Adds report filtering by validity status to the Vulnerability Report for rapid triage of leaked secrets 18.7 · Dec 2025 · source · release history
-
severity_thresholdconfig key in Operational Container Scanning filters vulnerability reports by severity level 18.4 · Sep 2025 · source · release history -
Adds
initialDetectedPipelineandlatestDetectedPipelinefields to the Vulnerability GraphQL API to retrieve commit information when vulnerabilities were introduced and last detected 18.2 · Jul 2025 · source · release history
IDE agentic integration shipped Provides access to agentic chat, flows, and code assistance via MCP in VS Code and JetBrains, including local knowledge graph indexing for repository context.
Also counts toward: Built-in AI assistant
release 9 total
-
Triggers reviewer suggestions automatically when a merge request is created, whether in draft or ready state, surfacing recommendations in a dedicated panel with one-click assignment.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Get every merge request in front of the right reviewer, faster (2026-10-15) · Oct 2026
· source
· release history
- Explains the reasoning behind each reviewer recommendation so authors can approve or override suggestions with full context. Get every merge request in front of the right reviewer, faster (2026-10-15) · Oct 2026 · source · release history
- Introduces toolsets so teams can configure which groups of tools the MCP server returns, with code security and wikis available as opt-in groups and most groups on by default. Connect your agents to your software lifecycle with the GitLab MCP server (2026-10-15) · Oct 2026 · source · release history
-
Adds
gitlab.featureFlags.flowBuildersetting in VS Code to enable the GitLab flow builder beta 19.4 · Sep 2026 · source · release history - Adds support for toggling the GitLab MCP server independently from Agent Platform settings 19.2 · Jul 2026 · source · release history
-
Adds
gitlab-duoCLI with interactive chat, headless CI/CD mode, and Model Context Protocol (MCP) connections support 19.2 · Jul 2026 · source · release history
Merge request approval workflows shipped Enforces review policies by tracking and managing approvals based on roles and unified assignment rules.
Also counts toward: GraphQL API support, Role-based access control
release 9 total
-
Enables automatic Code Review Flow at the project, group, or instance level so every merge request is reviewed without manual assignment, with settings that cascade down the hierarchy.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Unblock agentic software delivery with governed code review (2026-10-15) · Oct 2026
· source
· release history
- Adds Recommend Reviewers Flow, which suggests the smallest set of human reviewers who can satisfy code-owner and approval rules, factoring in expertise, workload, availability, and timezone. Unblock agentic software delivery with governed code review (2026-10-15) · Oct 2026 · source · release history
-
Adds
malware ruleto merge request approval policies to block malicious packages 19.4 · Sep 2026 · source · release history - Allows automatic assignment of Code Owners as reviewers in Merge Requests. 19.1 · Jun 2026 · source · release history
- Configures MR approval policies using Known Exploited Vulnerability (KEV) and EPSS data 18.11 · Apr 2026 · source · release history
-
Configure path exclusions in
CODEOWNERSfiles to ignore specific paths requiring Code Owner approval 17.10 · Mar 2025 · source · release history
Organization-level security dashboard shipped suggested A consolidated dashboard reachable from the Organization sidebar that aggregates vulnerability data across all top-level groups, showing a weighted risk score, trend charts over 30-, 60-, or 90-day windows, stale-finding and CWE pattern charts, and filtering by project or report type.
Suggested capability: Vulnerability prioritization. This is our guess, not confirmed.
release 8 total
-
Adds an organization-level security dashboard (beta on
GitLab.comUltimate) reachable via Organization > left sidebar > Secure > Security dashboard, consolidating vulnerability data across every top-level group without manual assembly.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Track organization-wide security risk in one dashboard (2026-10-08) · Oct 2026 · source · release history - Adds a Vulnerabilities over time view showing risk trend across the organization over selectable 30-, 60-, or 90-day windows. Track organization-wide security risk in one dashboard (2026-10-08) · Oct 2026 · source · release history
- Adds Vulnerabilities by age, Open vulnerabilities by severity, and Top 10 CWE charts to surface stale findings and recurring weakness patterns at the org level. Track organization-wide security risk in one dashboard (2026-10-08) · Oct 2026 · source · release history
- Supports dashboard filtering by project or by report type (e.g. SAST, dependency scanning) to scope the org-level risk view. Track organization-wide security risk in one dashboard (2026-10-08) · Oct 2026 · source · release history
- Introduces a risk score calculated from open vulnerability severity, age, KEV list membership, and EPSS score, giving security leaders a weighted prioritization signal rather than a raw count. Track organization-wide security risk in one dashboard (2026-10-08) · Oct 2026 · source · release history
- Exports security dashboards as PDFs 18.11 · Apr 2026 · source · release history
example
-
Navigate to the new org-level security dashboard to see consolidated risk score and vulnerability charts across all top-level groups — no spreadsheet assembly required.
1. In GitLab, go to Settings > General > Advanced and use 'Create Organizations' to confirm your Organization with multiple top-level groups exists. 2.Track organization-wide security risk in one dashboard (2026-10-08) · Oct 2026 · source
CI dependency management shipped Allows defining explicit dependencies between jobs in the CI configuration to control which artifacts are downloaded for each job execution.
Also counts toward: CI/CD pipeline integration
release 9 total
- API security testing findings include remediation guidance for checks like SQL injection, CORS, and HTML injection 19.0 · May 2026 · source · release history
-
Introduces the
$[[matrix.VARIABLE]]expression in Beta to create dynamic dependencies withinneeds:[parallel:matrix]configurations 18.6 · Nov 2025 · source · release history -
Adds support for
protected Maven packagesvia protection rules that restrict who can push new versions of a package, preventing accidental overwrites. 17.11 · Apr 2025 · source · release history -
Adds
needskeyword support for parallel matrix jobs in CI/CD pipelines 16.3 · Aug 2023 · source · release history -
Exposes pipeline name via
$CI_PIPELINE_NAMEpredefined variable 16.3 · Aug 2023 · source · release history -
Implements
needs:job:optionalfor CI pipelines to allow flexible job dependencies. 13.10.0 · Mar 2021 · source · release history
Multi-cluster Kubernetes management shipped Enables managing multiple Kubernetes clusters within GitLab core, removing previous Enterprise Edition restrictions.
Also counts toward: Web management console
release 9 total
- Adds Zero Downtime Upgrades support for Cloud Native Hybrid deployments on Kubernetes 18.9 · Feb 2026 · source · release history
- Adds full support for Kubernetes version 1.31 17.7 · Dec 2024 · source · release history
-
Adds
environment.kubernetes.agentsyntax to select a GitLab agent in CI/CD jobs 17.6 · Nov 2024 · source · release history - Adds ability to suspend or resume Flux reconciliation directly from the GitLab UI dashboard. 17.5 · Oct 2024 · source · release history
- Adds full support for Kubernetes version 1.30. 17.3 · Aug 2024 · source · release history
- Adds Delete pod action directly from the Kubernetes dashboard UI within GitLab. 17.3 · Aug 2024 · source · release history
Self-hosted AI model support shipped Enables self-hosted Large Language Model support for GitLab Duo Code Suggestions and Chat, including specific models like Llama 3.
Also counts toward: Self-hosted deployment
release 8 total
-
Supports self-hosted models as the foundation for agentic code review, keeping inference under customer control for air-gapped or regulated environments.
Unblock agentic software delivery with governed code review (2026-10-15) · Oct 2026
· source
· release history
- Adds support for Amazon Bedrock Mantle as a self-hosted model provider for GitLab Duo Agent Platform 19.3 · Aug 2026 · source · release history
- Deprecated Devstral 2 model for GitLab Duo Agent Platform Self-Hosted 19.3 · Aug 2026 · source · release history
- Supports Mistral AI as a self-hosted LLM platform in the Duo Agent Platform 18.11 · Apr 2026 · source · release history
- Adds an AI gateway timeout setting configurable from 60 to 600 seconds for self-hosted models 18.7 · Dec 2025 · source · release history
- Mistral Codestral is supported for GitLab Duo Chat (Classic) on Self-Managed instances 18.5 · Oct 2025 · source · release history
Duo Agent Platform self-hosted deployment shipped Deploys the Duo Agent Platform on agency-controlled infrastructure, supporting air-gapped networks, data residency mandates, and policies that prohibit transmitting code to third-party APIs.
Also counts toward: Air-gapped deployment, CI/CD pipeline integration, Self-hosted deployment
release 8 total
-
Supports deployment on
GitLab.comand on S3-compatible storage in customer-controlled infrastructure, including air-gapped data centers, preserving data sovereignty. Scaling Git for the agentic software factory (2026-10-13) · Oct 2026 · source · release history - Delivers stateless compute scaling horizontally against shared object storage, supporting thousands of concurrent agents working against large monorepos. Scaling Git for the agentic software factory (2026-10-13) · Oct 2026 · source · release history
-
Enables
GitLab Duo Agent Platform Self-Hosteddeployment on agency-controlled infrastructure, supporting air-gapped networks, data residency mandates, and policies barring code transmission to third-party APIs.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitLab and Claude Code: Fast, compliant AI (2026-09-29) · Sep 2026 · source · release history - Supports running AI models on GPU-enabled virtual machines in a private cloud for self-managed inference without dedicated hardware costs. GitLab and Claude Code: Fast, compliant AI (2026-09-29) · Sep 2026 · source · release history
- GitLab Duo Agent Platform for Self-Hosted (offline licensing) is generally available, supporting compatible models and AWS Bedrock/Azure OpenAI configurations. 18.8 · Jan 2026 · source · release history
- Adds vulnerability management policies to auto-dismiss irrelevant vulnerabilities based on file path, directory, or identifier (CVE, CWE, OWASP). 18.8 · Jan 2026 · source · release history
Secret Push Protection shipped suggested Blocks commits containing detected secrets upon push to GitLab.com and Dedicated instances.
Suggested capability: Static application security testing. This is our guess, not confirmed.
Also counts toward: GraphQL API support, REST API, SaaS deployment
release 8 total
- Adds instance-level enforcement setting for Secret Push Protection Co-Create: Building GitLab with our users (2026-09-10) · Sep 2026 · source · release history
- Generates audit events for fail-open scenarios in Secret Push Protection (ruleset errors, timeouts, etc.) 19.3 · Aug 2026 · source · release history
-
secret.validity_checksfeature in beta displays the active status of detected GitLab secrets to aid triage 18.5 · Oct 2025 · source · release history - Enables enabling secret push protection on all projects in a group via REST API and GraphQL API 17.7 · Dec 2024 · source · release history
- Adds audit events for secret push protection exclusions 17.6 · Nov 2024 · source · release history
- Updates application settings REST API to enable Secret Push Protection programmatically 17.6 · Nov 2024 · source · release history
CI/CD OIDC identity token support shipped Enables job environments to request and use OpenID Connect (OIDC) identity tokens for secure, short-lived authentication with external providers.
Also counts toward: CI/CD pipeline integration
release 8 total
-
Adds
id_tokenskeyword to custom agent configurations for authenticating with third-party OIDC services 19.2 · Jul 2026 · source · release history -
id_token_expirationconfig attribute to configure duration of ID tokens when GitLab acts as an OIDC provider 17.10 · Mar 2025 · source · release history - Adds admin setting to enforce CI/CD job token allowlist on self-managed instances 17.6 · Nov 2024 · source · release history
- Supports workload identity federation for Google Cloud authentication without service account keys. 16.11 · Apr 2024 · source · release history
- Adds filtering of streaming audit events by sub-group or project at the group level 16.8 · Jan 2024 · source · release history
-
Set
id_tokensas a global default in.gitlab-ci.ymlto apply OIDC token configuration to all jobs automatically 16.4 · Sep 2023 · source · release history
Pipeline schedule management shipped Allows creating and configuring pipeline schedules via API or configuration, supporting variable overrides for automated timing.
Also counts toward: CI/CD pipeline integration, REST API, Scheduled jobs
release 8 total
- Adds beta scheduled pipeline execution policies with time zone and snooze support. 19.1 · Jun 2026 · source · release history
- Adds dynamic input options in CI/CD pipelines to enable cascading dropdowns in the web interface 18.7 · Dec 2025 · source · release history
-
environment:deployment_tierfield now supports CI/CD variable expansion for dynamic configuration 18.5 · Oct 2025 · source · release history - The scheduled label/badge of delayed jobs is renamed to delayed. 11.5.0 · Nov 2018 · source · release history
- Allow pipelines to schedule delayed job runs 11.4.0 · Oct 2018 · source · release history
- Pipeline schedules support setting variable values via the API 10.0.0 · Sep 2017 · source · release history
GitLab Duo Chat Beta for Premium users shipped Provides a chat interface to explain issues, generate code, and answer DevSecOps questions.
Also counts toward: Built-in AI assistant, Self-hosted deployment
release 8 total
- Adds support for the AGENTS.md specification in GitLab Duo Chat (Agentic) in IDEs 18.7 · Dec 2025 · source · release history
- Adds the ability to select AI models (Claude, GPT, etc.) from a dropdown in the GitLab Duo Chat panel for VS Code and JetBrains IDEs 18.6 · Nov 2025 · source · release history
- Adds support for Anthropic Claude Sonnet 3.7 as the base model for GitLab Duo Chat, replacing Claude 3.5 Sonnet. 17.11 · Apr 2025 · source · release history
-
Adds
/helpcommand in GitLab Duo Chat to explore features 17.7 · Dec 2024 · source · release history - Enables self-hosted large language models as the source for GitLab Duo Chat and Code Suggestions on self-managed instances 17.6 · Nov 2024 · source · release history
- Makes GitLab Duo Chat available in JetBrains IDEs alongside UI, Web IDE, and VS Code. 16.11 · Apr 2024 · source · release history
Secure Files management shipped A dedicated interface and data model within Group settings for uploading, storing, and managing encrypted secret files accessible to CI jobs.
Also counts toward: CI/CD pipeline integration, Self-hosted deployment, Web management console
release
-
Declares secrets in
.gitlab-ci.ymlusing thesecrets:keyword, injecting values only into jobs that declare them and fall within scope (branch, protected-branch flag,production/*environment wildcards), and allows projects to inherit secrets defined in parent groups so a shared credential can be defined once… GitLab Secrets Manager: Govern secrets like your code (2026-10-15) · Oct 2026 · source · release history -
Adds
Secure > Secrets Managernavigation in top-level group settings onGitLab.com, with a 30-day / 500-credit free trial via Start 30-day trial, and is generally available for GitLab Premium and Ultimate onGitLab.comand GitLab Self-Managed (19.5), billed at 1 credit per secret per month and 1 credit per 2,500… GitLab Secrets Manager: Govern secrets like your code (2026-10-15) · Oct 2026 · source · release history -
Adds new integrations for secrets access: Kubernetes secret sync via External Secrets Operator (ESO) that re-fetches on a set interval and updates the Kubernetes Secret in-place without a pipeline run, Terraform and OpenTofu support as a data source at plan or apply time (keeping credentials out of
.tfvarsfiles and… GitLab Secrets Manager: Govern secrets like your code (2026-10-15) · Oct 2026 · source · release history - Prompts users to set a rotation reminder at secret creation time (dynamic/ephemeral credentials coming soon), and includes a secret audit tool for CI/CD variables that flags variables likely to hold credentials, enabling targeted migration. GitLab Secrets Manager: Govern secrets like your code (2026-10-15) · Oct 2026 · source · release history
- Streams every secret create, read, update, and delete event — including pipeline and job IDs — to audit event destinations and the GitLab audit trail, and encrypts secrets at rest with AES-256-GCM via OpenBao, keeping plaintext out of the GitLab application layer. GitLab Secrets Manager: Govern secrets like your code (2026-10-15) · Oct 2026 · source · release history
- Introduces the Secure Files data model and a dedicated file uploader UI component within the Group settings interface 14.7.0 · Jan 2022 · source · release history
example
-
Enable Secrets Manager and start the 30-day free trial on
GitLab.comfor a top-level group.1. Navigate to your top-level group in GitLab.com. 2. In the left sidebar, select Secure > Secrets Manager. 3. Click 'Start 30-day trial' to activate 500 evaluation credits.GitLab Secrets Manager: Govern secrets like your code (2026-10-15) · Oct 2026 · source
Bring-your-own-model configuration shipped Customers can connect their preferred model providers to the AI Gateway under their own data classification rules and existing model commitments.
release 7 total
- Adds Gemini 4 Argon as a selectable model on GitLab Duo Agent Platform, optimized for long-running, multi-step agentic tasks across the software lifecycle.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Gemini 4 Argon on GitLab: Built for long-running agentic work (2026-10-14) · Oct 2026 · source · release history
-
Introduces three GitLab-managed open-weight models —
GLM 5.3, Kimi K3, andMiniMax M3— hosted in Duo Agent Platform as lower-cost alternatives to frontier models.
Make every AI credit count: See, cap, and reduce agent spend (2026-10-13) · Oct 2026
· source
· release history
- GitLab Dedicated for Government customers can deploy the AI Gateway for Duo Agent Platform inside their own single-tenant environment and connect the model provider of their choice, including Amazon Bedrock, with inference staying in the chosen region under existing SLA, encryption, and change-control policies. GitLab and Claude Code: Fast, compliant AI (2026-09-29) · Sep 2026 · source · release history
- Enables bring-your-own-model configuration, letting customers connect preferred model providers under their own data classification rules and existing commitments. Run agentic software delivery inside the boundaries you already trust (2026-08-20) · Aug 2026 · source · release history
- Introduces allowlist controls and organization-wide default models for Agentic Chat. 19.1 · Jun 2026 · source · release history
-
Dependency scanning template
Jobs/Dependency-Scanning.v2.gitlab-ci.ymlis released for generating component vulnerability reports 18.5 · Oct 2025 · source · release history
Alert management dashboard and API shipped Provides a dedicated table, GraphQL API, and external webhook ingestion for tracking and correlating security alerts.
Also counts toward: GraphQL API support
release 7 total
- Adds Container Scanning for Registry in Ultimate tier to automatically scan container images pushed to the registry upon tag detection. 17.1 · Jun 2024 · source · release history
- Audit events now capture deployment approval and approval rule changes for protected environments. 16.5 · Oct 2023 · source · release history
- Adds Streaming audit event filtering UI to filter audit event types by area of GitLab without using the GraphQL API. 16.2 · Jul 2023 · source · release history
-
Add
deduplicatedcolumn tosecurity_findingstable along with the compound index onscan_idanddeduplicatedand remove the index onscan_id. 13.4.0 · Sep 2020 · source · release history -
Adds
Allow generic endpoint to receive alerts from external Prometheus.for Alert Management 13.1.0 · Jun 2020 · source · release history -
Alert Management table and GraphQL API endpoint
alertstrack and query security alerts 13.0.0 · May 2020 · source · release history
Agentic Chat shipped A conversational agent accessible from the GitLab UI and major IDEs that lets practitioners query merge requests, issues, and pipeline data in natural language, with a ready-made AI Resource Library of reusable prompts.
Also counts toward: CI/CD pipeline integration, Built-in AI assistant, Natural-language query
release
- Query blast radius in plain language via GitLab Duo Agentic Chat — for example, ask it to 'Use Orbit to map the blast radius of PHP in this group. List every project that contains PHP code, grouped by subgroup, with owners.' GitLab Orbit: Find vulnerability blast radius without the manual hunt (2026-10-29) · Oct 2026 · source · release history
-
Adds Agentic Chat via
GitLab Duo sidebar > Add new chat, letting practitioners query merge requests, issues, and pipeline data in natural language; available in the GitLab UI, VS Code, JetBrains IDEs, and Visual Studio with the Agentic toggle enabled. Three developer tasks worth handing to an agent (2026-10-19) · Oct 2026 · source · release history -
Adds an AI Resource Library of ready-made prompts (e.g.
Summarize Recent Changes to MR/Issue, Debug Failing Pipeline) for use with Agentic Chat. Three developer tasks worth handing to an agent (2026-10-19) · Oct 2026 · source · release history
example
-
Collect every container scanning finding for a specific CVE across the group via Agentic Chat (requires Ultimate and Security Manager role).
In GitLab Duo Agentic Chat, type: Collect every container scanning finding for CVE-2026-109618 and CVE-2026-109619 across the group from the vulnerability report.GitLab Orbit: Find vulnerability blast radius without the manual hunt (2026-10-29) · Oct 2026 · source -
Map every project in a group that uses PHP, grouped by subgroup with owners named, during a vulnerability triage.
In GitLab Duo Agentic Chat, type: Use Orbit to map the blast radius of PHP in this group. List every project that contains PHP code, grouped by subgroup, with owners.GitLab Orbit: Find vulnerability blast radius without the manual hunt (2026-10-29) · Oct 2026 · source -
Find all Dockerfiles that pull a PHP base image across the entire top-level group using exact regex search alongside Orbit.
lang:Dockerfile ^FROM.*phpGitLab Orbit: Find vulnerability blast radius without the manual hunt (2026-10-29) · Oct 2026 · source
Merge train status shipped Exposes the current state of merge trains through API endpoints to track protected branch integration progress.
Also counts toward: REST API
release
- Adds configurable merge train pipeline limits via project settings or admin area Co-Create: Building GitLab with our users (2026-09-10) · Sep 2026 · source · release history
- Adds an official Code intelligence CI/CD component supporting Go 1.21+, TypeScript, and JavaScript 17.4 · Sep 2024 · source · release history
-
Adds
connectcommand generation via the Kubernetes dashboard or agent list for terminal access to clusters. 17.3 · Aug 2024 · source · release history -
Enable
fast_forward_merge_trains_supportfeature flag for fast-forward merge support in merge trains 16.4 · Sep 2023 · source · release history -
Add Merge trains GET API (
GET /api/v4/merge_trains/:project_id) to GitLab Enterprise Edition for querying merge train status. 15.6.0 · Nov 2022 · source · release history -
GET /merge_trainspublic API endpoint to list merge train entries 12.9.0 · Mar 2020 · source · release history
Self-hosted SAML Group Sync shipped Automatic mapping of remote SAML groups to local GitLab groups for self-managed instances.
Also counts toward: Self-hosted deployment
release
-
Supports LDAP group sync configuration of the Auditor role via
audit_groupsetting 19.3 · Aug 2026 · source · release history - Allows automatic Duo Pro/Enterprise seat assignment for users synced via SAML Group Sync. 17.11 · Apr 2025 · source · release history
- Adds SAML Group Sync support for mapping custom roles in SAML SSO 16.8 · Jan 2024 · source · release history
- Allows assigning a custom role as the default SAML SSO provisioned role 16.8 · Jan 2024 · source · release history
- Group Owners can programmatically delete SAML or SCIM identities using new API endpoints. 16.5 · Oct 2023 · source · release history
- Introduce self-managed SAML Group Sync to automatically map remote SAML groups to local GitLab groups 15.1.0 · Jun 2022 · source · release history
CI runner size tiers shipped Offers configurable compute sizes for SaaS runners to match job requirements and optimize resource usage.
release
- Enables Kubernetes runners to define Pod level resources for build pods. 18.10 · Mar 2026 · source · release history
- Configures task scaler reservation throttling in GitLab Runner 18.7 18.7 · Dec 2025 · source · release history
-
Enables
FF_TIMESTAMPSby default in GitLab Runner 18.7 18.7 · Dec 2025 · source · release history -
Provides small hosted runners on Linux Arm for all tiers on
GitLab.com17.7 · Dec 2024 · source · release history -
Adds
macos-15-xcode-16job image for macOS Sequoia 15 and Xcode 16 17.6 · Nov 2024 · source · release history -
Adds
xlargeand2xlargeSaaS runners on Linux 16.3 · Aug 2023 · source · release history
GPG commit signature verification shipped Verifies developer signatures on commits using GPG keys and subkeys, ensuring committer identity matches the signer.
Also counts toward: REST API
release
-
Enables web-based commit signing on
GitLab.com, available in group or project settings with a Verified badge 18.9 · Feb 2026 · source · release history -
Adds
GitLab Duo Chatin Beta for Gold tier to summarize issues, generate code, and answer DevSecOps questions within the UI 16.6 · Nov 2023 · source · release history - Add support for GPG subkeys in signature verification 10.1.0 · Oct 2017 · source · release history
-
New API endpoints for GPG key management (
/user/gpg_keys) 10.0.0 · Sep 2017 · source · release history - GPG signature verification semantics changed: the committer must match the signer for a valid signature 10.0.0 · Sep 2017 · source · release history
-
gpg_signed_commitsintegration to verify developer signatures on commits 9.5.0 · Aug 2017 · source · release history
Service accounts management shipped Provides UI navigation and statistics dashboards for creating, managing, and monitoring service account tokens.
Also counts toward: Web management console
release
-
Makes service accounts available during trials on
GitLab.comfor Silver and Gold tiers 18.7 · Dec 2025 · source · release history -
Adds
accessLevelsargument toprojectMembersfield in GraphQL API 18.1 · Jun 2025 · source · release history - Adds a statistics dashboard to Service Account token management showing active, expiring, revoked, and expired token counts. 17.11 · Apr 2025 · source · release history
-
Adds custom expiration date (
expires_at) support when rotating service account tokens 17.9 · Feb 2025 · source · release history - Adds badge to service accounts in users list 17.6 · Nov 2024 · source · release history
- Adds optional setting for top-level group Owners to create service accounts 17.6 · Nov 2024 · source · release history
Deploy token management shipped Allows creating, listing, and managing scoped deploy tokens for projects and groups via API and UI.
Also counts toward: REST API
release
- Adds new custom role permissions: Manage merge request settings, Manage integrations, Manage deploy tokens, and Read CRM Contacts. 17.1 · Jun 2024 · source · release history
-
Adds
GETAPI endpoints for managing Deploy Tokens 14.9.0 · Mar 2022 · source · release history -
GET /deploy_tokensendpoint for project deploy tokens 12.9.0 · Mar 2020 · source · release history -
GET /groups/:id/deploy_tokensendpoint for group deploy tokens 12.9.0 · Mar 2020 · source · release history -
POST /deploy_tokensto create project deploy tokens 12.9.0 · Mar 2020 · source · release history -
POST /groups/:id/deploy_tokensto create group deploy tokens 12.9.0 · Mar 2020 · source · release history
AI Governance Dashboard shipped A top-level group dashboard that gives a unified view of GitLab Duo Agent Platform agents and externally connected agents (Claude Code, Cursor, Codex), with role-based access, audit event storage, and SIEM streaming of agent session data.
Also counts toward: Administrative audit log, Role-based access control, SIEM forwarding
release
-
Adds Store AI audit events toggle (in Settings > GitLab Duo > Change configuration > Data and privacy) to enable persistent recording of every agent action as an audit event.
AI Governance: One view of agent activity (2026-10-20) · Oct 2026
· source
· release history
-
Adds
read_agent_artifactscustom role ability to grant dashboard access without requiring Owner role on a top-level group. AI Governance: One view of agent activity (2026-10-20) · Oct 2026 · source · release history - Enables streaming of agent audit events to a SIEM system and downloading an immutable session copy as evidence from any GitLab Duo Agent Platform session. AI Governance: One view of agent activity (2026-10-20) · Oct 2026 · source · release history
- Introduces the AI Governance Dashboard (beta), accessible at AI > Governance > Dashboard tab in a top-level group, giving a unified view of GitLab Duo Agent Platform agents and externally connected agents (Claude Code, Cursor, Codex). AI Governance: One view of agent activity (2026-10-20) · Oct 2026 · source · release history
example
-
Enable AI audit event storage so agent actions start being recorded — without this, the dashboard shows no history.
In your top-level group, go to Settings > GitLab Duo, select 'Change configuration', then enable 'Store AI audit events' under Data and privacy. Requires Owner or Security Manager role.AI Governance: One view of agent activity (2026-10-20) · Oct 2026 · source
External agent session capture shipped Captures sessions from external AI coding agents (Claude Code, Cursor, Codex) via CLI-installed hooks and a background job, making their activity visible in the AI Governance Dashboard alongside native GitLab Duo agents.
Also counts toward: Command-line interface
release
-
Adds
glab govern setup --agents codex,cursorto capture Cursor and Codex sessions via a background job that sends sessions every 30 minutes.
AI Governance: One view of agent activity (2026-10-20) · Oct 2026
· source
· release history
-
Adds
glab govern doctorsubcommand to verify that agent-capture setup is working correctly. AI Governance: One view of agent activity (2026-10-20) · Oct 2026 · source · release history -
Adds
glab govern setupsubcommand (requiresglabCLI 1.122.0+) to install Claude Code hooks and capture sessions for the AI Governance Dashboard.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ AI Governance: One view of agent activity (2026-10-20) · Oct 2026 · source · release history
example
-
Capture Claude Code, Cursor, and Codex sessions so all external agent activity shows up in the AI Governance Dashboard.
glab govern setup --agents codex,cursorAI Governance: One view of agent activity (2026-10-20) · Oct 2026 · source -
Confirm that agent-capture hooks are installed and sending sessions correctly before handing the dashboard to an auditor.
glab govern doctorAI Governance: One view of agent activity (2026-10-20) · Oct 2026 · source
Managed application management shipped Enables the creation, configuration, and lifecycle management of external integrations via API and Admin UI.
Also counts toward: REST API, Web management console
release
- Adds the User Applications REST API to programmatically manage user-owned OAuth applications Co-Create: Building GitLab with our users (2026-09-10) · Sep 2026 · source · release history
-
Adds
use_inherited_settingsparameter to the REST API of all integrations to toggle inheritance via API. 17.3 · Aug 2024 · source · release history - Exposes Applications API endpoint to renew application secrets programmatically. 16.11 · Apr 2024 · source · release history
- Adds REST API support to retrieve, update, or disable the GitLab for Slack app integration settings at the project level. 16.9 · Feb 2024 · source · release history
- Instance-level integration CRUD (add/edit/delete) via API and Admin UI 12.9.0 · Mar 2020 · source · release history
Branch listing by upstream relationship shipped Adds a `--forked` filter to git-branch(1) that lists only branches whose configured upstream matches a specified ref, remote name, or branch, and a `--delete-merged` flag that deletes all local branches already reachable from their configured upstream.
release
-
git-branch(1) adds the
--forkedlisting filter to identify branches whose upstream matches a provided ref What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history -
Adds
--forkedflag to git-branch(1) as a listing filter to show branches whose configured upstream matches a provided ref, remote name, or branch. What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history -
git-branch(1) adds the
--delete-mergedoption to delete branches whose tips are reachable from their configured upstreams What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history -
Adds
--delete-mergedflag to git-branch(1) to delete all local branches whose tips are reachable from their configured upstream, removing merged feature branches in one step. What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history
CI configuration linting shipped Validates CI/CD configuration syntax and rules before execution to prevent pipeline failures.
release
-
Adds new CI/CD variables
CI_JOB_RETRY_COUNTandCI_JOB_TAGS19.3 · Aug 2026 · source · release history - Makes the CI cache limit per job configurable by admins instead of using a hard-coded default. GitLab Patch Release: 19.0.2, 18.11.5, 18.10.8 · Jun 2026 · source · release history
-
CI/CD inputs support array index operator
[]to access specific elements within array inputs 19.0 · May 2026 · source · release history - API for Ci Lint 8.12.0 · Sep 2016 · source · release history
Clone override binary shipped A self-contained Go binary intercepts bare `git clone` calls and executes a fixed shallow-and-partial-clone sequence, applying the repo's policy file before any source hits disk, while passing through clones that already carry explicit flags or repos without a policy file.
release
-
Adds a self-contained Go binary (
git-clone-override-policy) that intercepts baregit clone <URL>calls and automatically executes a fixed 13-step shallow-and-partial-clone sequence, applying the repo's policy file before any source hits disk.
Avoid the massive end-to-end tax of default full history clones (2026-08-18) · Aug 2026
· source
· release history
-
Policy intercept is bypass-safe: any clone that already carries an option (
--depth,--filter, or any flag) passes through untouched; repos without a policy file also pass through with no behavioral change. Avoid the massive end-to-end tax of default full history clones (2026-08-18) · Aug 2026 · source · release history -
Add
$CI_ENVIRONMENT_URLto predefined CI/CD variables. 9.3.0 · Jun 2017 · source · release history
example
-
Run the override binary in place of
git cloneso the policy is enforced for a one-off zero-footprint clone without any global git config changes../git-clone-override-policy https://example.com/group/my-repo.gitAvoid the massive end-to-end tax of default full history clones (2026-08-18) · Aug 2026 · source
Granular Duo AI feature toggles shipped Programmatically enable or disable individual GitLab Duo AI features across projects, groups, or the entire instance via API.
Also counts toward: Scripting API
release
- Adds Always on availability mode for GitLab Duo to lock AI features centrally. 19.1 · Jun 2026 · source · release history
- Introduces group access control rules to define who can use GitLab Duo features within a group. 18.8 · Jan 2026 · source · release history
- Group/Application settings allow automatic Duo Code Review for multiple projects simultaneously 18.4 · Sep 2025 · source · release history
- Disable or enable GitLab Duo AI features for a project, group, or instance via the API. 16.10 · Mar 2024 · source · release history
Nested group hierarchy management shipped Allows organizing projects and groups into a nested tree structure, with API endpoints and UI controls for creating and listing subgroups.
Also counts toward: REST API
release
-
Adds the ability to
archivean entire group and all its subgroups/projects in one action 18.9 · Feb 2026 · source · release history -
Add
/groups/:id/subgroups endpoint to API 10.3.0 · Dec 2017 · source · release history - Add nested groups to the API. !9034 9.0.0 · Mar 2017 · source · release history
- Allow creating nested groups via UI. !8786 9.0.0 · Mar 2017 · source · release history
Per-group two-factor authentication requirement shipped Allows administrators to enforce two-factor authentication for all members at the group level.
Also counts toward: Multi-factor authentication
release
-
Restricts personal snippet creation for enterprise users on
GitLab.com, managed by Group Owners 18.9 · Feb 2026 · source · release history - Group Owners can disable SSH keys for all enterprise users in their group. 18.8 · Jan 2026 · source · release history
- Allows disabling OTP and WebAuthn devices independently 17.6 · Nov 2024 · source · release history
-
Enables per-group
2FArequirement. 9.1.0 · Apr 2017 · source · release history
Artifact Central package type support shipped Extends Artifact Central to support storing and managing Go packages and generic artifact types alongside existing container registry capabilities.
release
- Customizable detection logic for Advanced SAST allows creating custom security rules tailored to organization requirements 18.5 · Oct 2025 · source · release history
- Adds the PyPI Package Importer tool to import packages from any PyPI-compliant registry into GitLab. 16.2 · Jul 2023 · source · release history
- Adds support for Generic packages in the Package Registry 13.5.0 · Oct 2020 · source · release history
- Adds Go(lang) language support to Packages via the existing Package Registry UI 13.5.0 · Oct 2020 · source · release history
Pipeline execution policy management shipped Introduces `inject_policy` strategy and environment variable support for pipeline execution policies, replacing deprecated modes.
Also counts toward: CI/CD pipeline integration
release
- Scan execution policy templates (Merge request, Scheduled, Release) added to accelerate creation of security scan policies 18.3 · Aug 2025 · source · release history
-
Adds
variables_overrideconfiguration option for pipeline execution policies 18.1 · Jun 2025 · source · release history -
Introduces
inject_policystrategy for pipeline execution policies to enforce custom stages with DAG merging 17.9 · Feb 2025 · source · release history -
The
inject_cimode for pipeline execution policies is deprecated;inject_policyreplaces it as the new strategy 17.9 · Feb 2025 · source · release history
Issues Board view shipped Provides a Kanban-style board interface for managing issues, with API support for programmatic control.
Also counts toward: GraphQL API support, REST API
release
- Allows setting Work in Progress (WIP) limits by weight in addition to issue count on boards. 17.11 · Apr 2025 · source · release history
-
Expose
hide_backlog_listandhide_closed_listfields in project and group boards REST API 13.8.0 · Jan 2021 · source · release history - Add GraphQL mutations to reorder designs, update board list position/collapsed state, and move issues within board lists 13.3.0 · Aug 2020 · source · release history
- Adds Issue Board API support to manage boards programmatically. 8.13.0 · Oct 2016 · source · release history
Artifact retention control shipped Allows users to configure whether build artifacts are retained based on job status, such as keeping them only when a job succeeds or fails.
Also counts toward: REST API
release
- Adds support for the Known Exploited Vulnerabilities (KEV) Catalog in composition analysis via GraphQL 17.7 · Dec 2024 · source · release history
-
Adds new endpoint
/projects/:id/artifacts/downloadto download single artifact file for a ref 11.6.0 · Dec 2018 · source · release history - Remove support for legacy tar.gz pages artifacts 10.7.0 · Apr 2018 · source · release history
-
Add
artifacts:whenoption to.gitlab-ci.ymlto control artifact retention based on job status 8.9.0 · Jun 2016 · source · release history
Webhook custom header configuration shipped Define and attach custom HTTP headers to webhook payloads for external service authentication, with support for up to 20 headers.
Also counts toward: REST API, Outbound webhooks (the product notifies you)
release
- Allows setting custom webhook headers using the GitLab REST API. 17.1 · Jun 2024 · source · release history
-
custom_webhook_headersallows specifying custom HTTP headers for webhook payloads 17.0 · May 2024 · source · release history - Allows up to 20 custom headers to be added to webhooks for external service authentication. 16.11 · Apr 2024 · source · release history
- Adds webhook events for expiring group and project access tokens. 16.11 · Apr 2024 · source · release history
Container expiration policies shipped Allows configuring and managing expiration rules for container registry images via the GraphQL API.
Also counts toward: GraphQL API support
release
-
Allows setting SLSA 1.0 provenance via the
SLSA_PROVENANCE_SCHEMA_VERSION=v1variable in.gitlab-ci.yml16.7 · Dec 2023 · source · release history - Adds option in Container Scanning to exclude findings that the vendor has evaluated as not fixable 16.6 · Nov 2023 · source · release history
-
Adds
maximum decompressed file sizeapplication setting to configure import archive limits 16.3 · Aug 2023 · source · release history -
Adds
container expiration policyobjects and attributes via the GraphQL API 13.1.0 · Jun 2020 · source · release history
Merge request work-in-progress control shipped Allows developers to mark merge requests as Work In Progress (WIP) via web interface or CLI, hiding them from review boards while still open.
Also counts toward: Command-line interface
release
- Metrics dashboard annotations feature allows marking events on charts via GraphQL or API 13.0.0 · May 2020 · source · release history
-
Adds
Add metrics dashboard annotations to GraphQL APIto annotate charts with data points 12.10.0 · Apr 2020 · source · release history -
Adds
/wipslash command to toggle the Work In Progress status of a merge request. 8.13.0 · Oct 2016 · source · release history
example
-
Toggle the Work In Progress status of a merge request via CLI to hide it from review boards.
/wip8.13.0 · Oct 2016 · source
Agent action attribution & audit trail shipped Tracks and records agent decisions, instructions, and code changes to provide full auditability and reviewer context.
release
- GitLab Duo Agent Platform now gives each agent a composite identity limited to the permissions it shares with the requesting user, a sandbox destroyed when the task ends, and a full action record, with agents earning more autonomy only as controls at each stage are proven under the GitLab Security Standard. What happens when vulnerabilities are discovered faster than you can fix them? (2026-10-28) · Oct 2026 · source · release history
-
Flows API response includes a
web_urlfield linking to the agent session, enabling inspection of each step the flow took.
Extend GitLab Duo Agent Platform into your business systems (2026-10-27) · Oct 2026
· source
· release history
- Adds attribution and authorization of agent actions, preservation of instructions and decisions behind code changes, and reviewer context to focus human judgment. Scaling Git for the agentic software factory (2026-10-13) · Oct 2026 · source · release history
External secret manager integration shipped Connects CI/CD jobs to external vaults like Azure Key Vault to retrieve secrets securely during execution.
Also counts toward: CI/CD pipeline integration
release
- Provides a Secrets Manager API for runtime tools to authenticate with a service account or access token and receive a separate five-minute-valid token per fetch, and issues short-lived tokens bound to each job's identity so jobs fetch values directly from OpenBao. GitLab Secrets Manager: Govern secrets like your code (2026-10-15) · Oct 2026 · source · release history
- Adds Google Cloud Secret Manager support for retrieving secrets in CI/CD jobs 16.8 · Jan 2024 · source · release history
- Adds Azure Key Vault secrets manager integration for CI/CD jobs 16.3 · Aug 2023 · source · release history
Merged feature branch cleanup shipped Deletes all local feature branches that have already been merged into origin/main, including branches forked from it rather than merged locally, in a single operation.
release
-
Adds
--delete-mergedflag to git-branch(1) to delete all local branches whose tips are reachable from their configured upstream, removing merged feature branches in one step. What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history
example
-
Clean up all local feature branches that have already been merged into origin/main, including branches forked from it rather than merged locally.
git branch --delete-merged originWhat's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source -
Delete all feature branches that have been fully merged into the main integration branch.
git branch --delete-merged originWhat's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source
Remote object metadata fetch shipped Adds a `remote-object-info` command to git-cat-file(1)'s `--batch-command` mode that retrieves object size and type over Git protocol v2 without downloading the full object.
Also counts toward: Command-line interface
release
-
git-cat-file(1) adds the
remote-object-infocommand to its--batch-commandmode for fetching object metadata without downloading the full object What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history -
Adds
remote-object-infocommand to git-cat-file(1)'s--batch-commandmode to fetch object metadata (size, type) over Git protocol v2 without transferring the full object. What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history
example
-
Fetch metadata for a blob in a partial clone without downloading the object itself to save bandwidth.
echo "remote-object-info origin <blob-hash>" | git cat-file --batch-commandWhat's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source
Repository path info fields shipped Extends the `git repo info` subcommand with `path.gitdir` and `path.commondir` fields in both absolute and relative forms, exposing repository layout details programmatically.
Also counts toward: Command-line interface
release
-
Extends
git repo infosubcommand withpath.gitdirandpath.commondirfields, each available in both absolute and relative forms. What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history -
git repo infoextends output withpath.gitdir.absolute,path.gitdir.relative,path.commondir.absolute, andpath.commondir.relativefields What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history - Expose Prometheus metrics with full parity to the existing InfluxDB metrics set. 10.2.0 · Nov 2017 · source · release history
OAuth code push shipped Allows OAuth client applications to push code directly to the repository.
release
-
Adds
mcpscope support to OAuth applications via the Admin area API 19.3 · Aug 2026 · source · release history - Allows instance administrators to set custom OAuth access token lifetimes (300–7200 seconds). 19.1 · Jun 2026 · source · release history
- Allow OAuth clients to push code 9.2.0 · May 2017 · source · release history
Per-repo git config scoping shipped A `[git_config]` block in the policy file applies large-transfer tuning settings to the cloned repository only, without modifying the user's global git configuration.
release
-
Supports
[git_config]block to scope large-transfer tuning (core.compression,http.postBuffer,http.lowSpeedLimit,http.lowSpeedTime,pack.windowMemory,pack.packSizeLimit,pack.threads) to the cloned repo without affecting global git config.
Avoid the massive end-to-end tax of default full history clones (2026-08-18) · Aug 2026
· source
· release history
- Brings the GitLab MCP server into Beta, enabling AI assistants to interact with projects, issues, MRs, and pipelines via MCP protocol 18.6 · Nov 2025 · source · release history
-
The
allow_overflowoption inTimeHelper.duration_in_numbersis dropped. 11.5.0 · Nov 2018 · source · release history
Secret detection analytics shipped Identifies and reports exposed credentials like API keys across pipeline execution and client-side operations, extending visibility beyond push-time protection.
Also counts toward: CI/CD pipeline integration
release
- Enables full branch secret detection scanning from divergence point to latest commit. 19.1 · Jun 2026 · source · release history
- Adds search and filter capabilities to the Credentials Inventory, including expiration windows 17.9 · Feb 2025 · source · release history
- Adds detection of Anthropic API keys in both pipeline and client-side Secret Detection 17.4 · Sep 2024 · source · release history
Vulnerability management policies shipped Enables automated dismissal of irrelevant vulnerabilities based on configurable file paths, directories, or identifiers (CVE, CWE, OWASP).
release
- Adds vulnerability management policies to auto-dismiss irrelevant vulnerabilities based on file path, directory, or identifier (CVE, CWE, OWASP). 18.8 · Jan 2026 · source · release history
- Enables using the API to query a filtered list of policy violations on the default branch in a project 18.7 · Dec 2025 · source · release history
- Extends security policy scope to include groups/subgroups for targeted enforcement. 17.5 · Oct 2024 · source · release history
Security inventory and posture visibility shipped Offers a centralized Security Inventory view and dashboard modules to assess security coverage, configuration status, dependency paths, and risk scores across projects.
release
- Adds a new security dashboard enabled by default on GitLab Dedicated and GitLab Self-Managed 18.7 · Dec 2025 · source · release history
- Adds a risk score module to the new security dashboards that calculates estimated risk based on a GitLab algorithm 18.7 · Dec 2025 · source · release history
- Adds Security Inventory beta for Ultimate tier users to provide a centralized view of security posture, coverage gaps, and configuration status across all projects and groups 18.2 · Jul 2025 · source · release history
GitLab Workspaces general availability shipped Promote GitLab Workspaces to general availability with production-ready error handling, private project access, and SSH connectivity.
release
-
shared_namespaceagent config field enables GitLab Workspaces to use a shared Kubernetes namespace 18.0 · May 2025 · source · release history - Adds support for private container registries in workspaces via image pull secrets 17.6 · Nov 2024 · source · release history
- Marks Workspaces as generally available with error handling, private project, and SSH support 16.8 · Jan 2024 · source · release history
CI runner token management shipped Administrative capabilities to filter CI runner tokens by status and configure their expiration intervals.
Also counts toward: GraphQL API support, Web management console
release
-
@GitLabDuomentioned as a reviewer or in comments to trigger Duo Code Review beta on merge requests (Ultimate tier) 17.10 · Mar 2025 · source · release history -
Enables filtering of CI runner tokens by their current status (
active,revoked) in the admin UI 14.7.0 · Jan 2022 · source · release history -
Adds
runner_token_expiration_intervalfield to theApplicationSettingGraphQL schema to control CI runner token lifetimes 14.7.0 · Jan 2022 · source · release history
GitLab Pages hosting shipped Enables static site publishing directly from the repository, making the capability available across all editions.
Also counts toward: CI/CD pipeline integration
release
- Adds ability to restrict GitLab Pages access at the group level via a single setting 17.9 · Feb 2025 · source · release history
-
Allows using
pagesattribute in any CI/CD job instead of naming a job pages 17.6 · Nov 2024 · source · release history - Added GitLab Pages to CE. 8.17.0 · Feb 2017 · source · release history
DORA metrics compliance shipped Measurement of the `time_to_restore_service` metric to assess incident recovery speed in alignment with DORA standards.
release
- Adds DORA Performers score panel to the Value Streams Dashboard 16.8 · Jan 2024 · source · release history
- Adds basic DORA data models to track DevOps metrics 15.4.0 · Sep 2022 · source · release history
-
Adds the
time_to_restore_servicemetric in compliance with DORA standards 14.9.0 · Mar 2022 · source · release history
Password reset email expansion shipped Allow users to initiate password resets by entering any email address associated with their account instead of requiring a single registered email.
release
- User password reset now accepts multiple email addresses associated with the same account. 16.3.7 · Jan 2024 · source · release history
- User password reset accepts multiple email addresses 16.4.5 · Jan 2024 · source · release history
- Allows user password reset to accept multiple email addresses for the same account. 16.1.6 · Jan 2024 · source · release history
Harbor registry integration shipped Support for browsing and using Harbor registries as a container registry backend within the platform.
release
-
Adds a
harbor registry tags pageto view and manage tags within Harbor registries 15.4.0 · Sep 2022 · source · release history - Adds Harbor as a supported container registry integration type 14.9.0 · Mar 2022 · source · release history
-
Enables filtering of CI runner tokens by their current status (
active,revoked) in the admin UI 14.7.0 · Jan 2022 · source · release history
Hashed file storage shipped Implements hashed storage for repository files and attachments to improve scalability and performance.
release
- Add support for specifying AWS S3 Server Side Encryption (AWS-KMS) 13.3.0 · Aug 2020 · source · release history
- Add Azure Blob Storage support for object storage 13.3.0 · Aug 2020 · source · release history
- Introduce Hashed Storage support for file attachments in projects. 10.2.0 · Nov 2017 · source · release history
Repository archive downloads shipped Enables downloading project archives in various formats through dedicated API endpoints for export or backup.
Also counts toward: REST API
release
- Add an API endpoint to download git repository snapshots. 10.7.1 · Apr 2018 · source · release history
-
Add
GET /projects/:id/exportAPI endpoint to initiate project exports 10.6.0 · Mar 2018 · source · release history - Add support of Mermaid (generation of diagrams and flowcharts from text) 10.3.0 · Dec 2017 · source · release history
Fix CI/CD Pipeline Flow shipped An agentic flow triggered from a merge request or the Pipelines list that reads pipeline logs and proposes a fix by posting inline suggestions, opening a new merge request, or adding next-step comments.
Also counts toward: CI/CD pipeline integration, Built-in AI assistant
release
- Adds Fix CI/CD Pipeline Flow: select Fix pipeline with Duo from a merge request's Overview or Pipelines tab to have an agent read pipeline logs and propose inline code suggestions, open a new merge request with a fix, or post next-step comments. Three developer tasks worth handing to an agent (2026-10-19) · Oct 2026 · source · release history
-
Adds Fix pipeline with Duo for pipelines not tied to a merge request via
Build > Pipelines, producing a new merge request with the proposed fix. Three developer tasks worth handing to an agent (2026-10-19) · Oct 2026 · source · release history
Commit drop and history rewrite shipped Removes a specified commit and rebases its descendants in a single non-interactive step, exposed as a `drop` subcommand of git-history(1).
Also counts toward: Command-line interface
release
-
git-history(1) learns a new
dropsubcommand for removing commits in one line What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history
example
-
Remove a commit and rebase its descendants in a single step without interactive editing.
git history drop <commit>What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source
git refs management subcommands shipped Adds `create`, `update`, `rename`, and `delete` subcommands to git-refs(1), with optional expected-old-value validation on `update` and `delete` for safe concurrent ref operations.
Also counts toward: Command-line interface
release
-
git-refs(1) gains
create,delete,update, andrenamesubcommands for modifying references directly What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history -
Adds
create,update,rename, anddeletesubcommands to git-refs(1), withupdateanddeleteaccepting an optional expected old value for validation. What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history
Linearized history replay shipped Adds a `--linearize` flag to git-replay(1) that flattens merge commits when rebasing a commit range, enabling replay of non-linear history as a straight sequence.
Also counts toward: Command-line interface
release
-
Adds
--linearizeflag to git-replay(1) to enable rebasing commit ranges that contain merge commits by flattening the history. What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history -
git replay(1) adds the
--linearizeflag to handle rebasing branches that contain merge commits What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history
Promisor blob pruning shipped Adds a `--drop-filtered` option to git-repack(1) that removes large promisor blobs exceeding a specified filter threshold from the local object store.
release
-
git-repack(1) adds the
--drop-filteredoption to remove large promisor blobs above a specified filter from the local store What's new in Git 2.56.0? (2026-09-28) · Sep 2026 · source · release history -
Allow
CI_JOB_TOKENfor authenticating to the Terraform state API 13.1.0 · Jun 2020 · source · release history
Agent Skills specification support shipped Allows agents to load specialized workflows triggered by name, file path, or slash commands.
Also counts toward: Command-line interface
release
-
Adds
/goalslash command in GitLab Duo CLI to delegate open-ended objectives to a governed local flow 19.4 · Sep 2026 · source · release history - Supports the Agent Skills specification, allowing agents to load specialized workflows triggered by name, file path, or slash commands. 18.10 · Mar 2026 · source · release history
Repository X-Ray analysis shipped suggested Runs automated repository analysis background jobs on default branch commits to surface structural, dependency, and health insights.
Suggested capability: Static application security testing. This is our guess, not confirmed.
release
- Extends GitLab Orbit with Scala language support for indexing and code-graph definitions Co-Create: Building GitLab with our users (2026-09-10) · Sep 2026 · source · release history
- Automates Repository X-Ray background jobs on default branch commits 17.6 · Nov 2024 · source · release history
Automated dependency version bumping shipped Automatically bumps dependency versions in CI/CD pipelines for both vulnerability remediation and breaking change resolution.
Also counts toward: CI/CD pipeline integration
release
- Adds Dependency scanning auto-remediation (Beta) for automated dependency version bumps and Agentic Breaking Change Resolution 19.2 · Jul 2026 · source · release history
example
-
Switch the agent to use the new faster model for dependency updates via the UI.
In Duo Agent Platform settings, select GPT-6 Astra from the model pickerGPT-6 Astra on GitLab: Faster runs, fewer tokens used (2026-09-08) · Sep 2026 · source
CI Component usage analytics shipped Shows which projects use each component in the CI/CD Catalog and their versions.
Also counts toward: GraphQL API support
release
- Component usage analytics in CI/CD Catalog shows exactly which projects use each component and their versions 19.0 · May 2026 · source · release history
- Adds a GraphQL query to track CI/CD component usage across projects within pipelines 17.7 · Dec 2024 · source · release history
Container virtual registries shipped Allows creating a unified endpoint to pull from multiple upstream container registries, with support for group-level management.
Also counts toward: REST API, Scripting API, Web management console
release
- Provides a dedicated group-level UI to create and manage container virtual registries without API calls. 18.10 · Mar 2026 · source · release history
-
Adds
container_virtual_registriesbeta API for creating a unified endpoint to pull from multiple upstream container registries 18.9 · Feb 2026 · source · release history
Secret false positive detection shipped Provides AI-powered context and confidence scores to identify false positive secrets in the vulnerability report.
Also counts toward: ML-based detection
release
- Introduces AI-powered secret false positive detection (beta) for Critical and High severity secrets, providing contextual reasoning and confidence scores in the vulnerability report. 18.10 · Mar 2026 · source · release history
- Integrates secret validity checks with Google Cloud, AWS, and Postman vendor integrations 18.7 · Dec 2025 · source · release history
CI/CD job metrics and analytics shipped Provides UI dashboards and UTC timestamps in job logs to track execution performance and identify pipeline bottlenecks.
release
- Adds CI job log timestamps (UTC) to identify bottlenecks, requiring GitLab Runner 18.7+ 18.9 · Feb 2026 · source · release history
- Adds UI for viewing CI/CD job metrics and analytics for projects in the UI 18.9 · Feb 2026 · source · release history
Programmatic Jira import shipped Allows triggering Jira imports via GraphQL mutations for integration with external automation workflows.
Also counts toward: GraphQL API support, Import from a competing product
release
- Enables import of repositories from Bitbucket Cloud using API tokens via the GitLab import API 18.9 · Feb 2026 · source · release history
- Allows Allow to start Jira import through graphql mutation for programmatic trigger of imports 12.10.0 · Apr 2020 · source · release history
Vulnerability by age analysis shipped Provides a dedicated chart in the security dashboard to analyze the duration of unresolved vulnerabilities.
release
- Adds Vulnerabilities by age chart to the Ultimate security dashboard for analyzing unresolved vulnerability duration 18.9 · Feb 2026 · source · release history
- Updates Vulnerabilities over time chart to exclude vulnerabilities that are no longer detected 18.9 · Feb 2026 · source · release history
CLI issue search shipped Provides a command-line interface to query and filter work items directly from the terminal.
Also counts toward: Command-line interface
release
- Expands Advanced Search to return matching results from both merge request descriptions and comments 18.7 · Dec 2025 · source · release history
- Add issue search slash command 8.15.0 · Dec 2016 · source · release history
Windows Server 2022 runner support shipped Provide officially supported runner images for Windows Server 2022 using the saas-windows-medium-amd64 tag.
release
- Adds Windows 11 2025 (25H2) support in GitLab Runner 18.7 18.7 · Dec 2025 · source · release history
-
Adds Windows 2022 support for SaaS runners using
saas-windows-medium-amd64tag 16.8 · Jan 2024 · source · release history
Maven dependency proxying shipped Provide a self-hosted Maven dependency proxy to cache and serve external Java repositories within the cyber tooling.
Also counts toward: Self-hosted deployment
release
- Adds Maven virtual registry in beta for aggregating upstream repositories behind a single endpoint 18.1 · Jun 2025 · source · release history
- Adds Maven dependency proxy for external Java repositories in GitLab Self-Managed 16.8 · Jan 2024 · source · release history
Custom merge method support shipped Enables configuring and applying custom merge strategies to repositories, moving this capability to the core edition.
release
- Configurable squash settings for each protected branch through branch rules 17.10 · Mar 2025 · source · release history
- Move Custom merge methods from EE to CE 10.1.0 · Oct 2017 · source · release history
Webhook mutual TLS support shipped Configure outgoing webhooks to enforce mutual TLS authentication by specifying client certificates in PEM format.
Also counts toward: Outbound webhooks (the product notifies you)
release
- Webhook triggers 60 and 30 days before access token expiry via extended webhook settings 17.10 · Mar 2025 · source · release history
- Configure webhooks to support mutual TLS by specifying a client certificate in PEM format. 16.10 · Mar 2024 · source · release history
Custom role permission tiers shipped Introduce granular permission types like Read Runners that can be assigned when building custom roles for the cyber tooling.
Also counts toward: Role-based access control
release
- Adds Read compliance dashboard permission for custom roles 17.9 · Feb 2025 · source · release history
- Adds Read Runners permission type available for creating custom roles. 17.3 · Aug 2024 · source · release history
Dynamic child pipelines shipped Allows CI/CD jobs to generate and trigger new pipelines dynamically from artifact content.
Also counts toward: CI/CD pipeline integration
release
- Adds FluxCD CI/CD component support for packaging Kubernetes manifests into OCI images 17.9 · Feb 2025 · source · release history
-
Dynamic child pipeline creation from CI/CD artifact content via
feature.dynamic_child_pipelineflag 12.9.0 · Mar 2020 · source · release history
Code coverage visualization shipped Displays test coverage reports, such as JaCoCo data, directly within the merge request diff view to provide developers with code coverage feedback during reviews.
release
- Makes JaCoCo test coverage visualization generally available in merge request diff view 17.6 · Nov 2024 · source · release history
- Adds JaCoCo coverage report visualization for merge requests as a beta feature 17.4 · Sep 2024 · source · release history
Model Registry shipped Stores, versions, and discovers machine learning models via UI or MLflow.
Also counts toward: Web management console
release
- Makes Model registry generally available with MLflow client integration and GitLab API support 17.6 · Nov 2024 · source · release history
- Adds Model registry in beta as a first-class concept for storing, versioning, and discovering machine learning models via UI or MLflow. 17.1 · Jun 2024 · source · release history
Task and OKR hierarchy display shipped Render parent-child ancestor hierarchies for Tasks and Objectives/Key Results in the project planning interface.
release
- Enables setting parent items for OKRs and tasks directly from child records. 17.3 · Aug 2024 · source · release history
- Adds ability to view ancestor hierarchy for Tasks and Objectives/Key Results 16.8 · Jan 2024 · source · release history
Pipeline email notifications shipped Delivers email alerts to users regarding the cyber tool pipeline status and events.
release
- Adds settings to disable diff previews in code review emails under groups and projects. 17.1 · Jun 2024 · source · release history
- Add pipeline email service 8.12.0 · Sep 2016 · source · release history
Repository storage migration API shipped Exposes an API endpoint to schedule and execute project repository storage moves.
Also counts toward: REST API
release
- Adds ability to cancel a running direct transfer migration via REST API. 17.1 · Jun 2024 · source · release history
- Add API to schedule project repository storage moves 13.1.0 · Jun 2020 · source · release history
Group-level analytics landing page shipped Present a centralized group dashboard featuring the Value Streams Dashboard and median time to merge metrics.
release
-
Value Streams Dashboard displays a new
median time to mergemetric 17.0 · May 2024 · source · release history - Introduces group-level landing page for Analytics Dashboards with Value Streams Dashboard 16.8 · Jan 2024 · source · release history
CI/CD token-based rules shipped Allows CI/CD pipeline rules to match based on the presence or value of specific variables, including tokens, enabling more dynamic job execution logic.
Also counts toward: CI/CD pipeline integration, REST API
release
-
Adds a new REST API endpoint to configure the CI/CD job token (
CI_JOB_TOKEN) scope programmatically, removing the need for GraphQL or UI only 16.1 · Jun 2023 · source · release history -
Adds the
tokensub-keyword inside CI/CDrulesconfig for token-based matching 15.7.0 · Dec 2022 · source · release history
Incident scheduling and oncall management shipped Provides data structures and tables for managing oncall rotations and participant schedules to automate incident response workflows.
Also counts toward: GraphQL API support
release
-
Add GraphQL mutation
onCallRotationand table for tracking on-call shifts to manage rotations programmatically 13.8.0 · Jan 2021 · source · release history - Adds oncall rotations and participants tables for incident management scheduling. 13.7.0 · Dec 2020 · source · release history
Custom Pages domain management shipped Provides API endpoints to configure and manage custom domains for GitLab Pages instances.
Also counts toward: REST API
release
-
Expose project_id on /api/v4/pages/domains.10.4.0 · Jan 2018 · source · release history - Add API endpoints for managing Pages Domains on GitLab Pages instances. 10.2.0 · Nov 2017 · source · release history
Image diff commenting shipped Enables users to add comments and view replaced file links specifically within image diffs during code review.
release
- Commenting on image diffs 10.1.0 · Oct 2017 · source · release history
- Add view replaced file link for image diffs 10.1.0 · Oct 2017 · source · release history
Secrets Manager shipped Limits each CI/CD pipeline job to only the credentials it explicitly requests and is authorized to use, so a compromised dependency can access only the secrets of the job it runs in.
Also counts toward: CI/CD pipeline integration
release
- GitLab adds Secrets Manager, which limits each pipeline job to only the credentials it explicitly requests and is authorized to use, so a compromised dependency can reach only the secrets of the job it runs in. What happens when vulnerabilities are discovered faster than you can fix them? (2026-10-28) · Oct 2026 · source · release history
Agent session live view shipped An AI > Sessions view that streams agent reasoning steps in real time while Fix CI/CD Pipeline Flow or Agentic Chat is running.
release
-
Adds
AI > Sessionsview to follow agent reasoning in real time while Fix CI/CD Pipeline Flow or Agentic Chat runs. Three developer tasks worth handing to an agent (2026-10-19) · Oct 2026 · source · release history
Isolated agent sessions shipped Runs agent experiments in isolated sessions that can be discarded safely while merging successful changes into existing workflows.
Also counts toward: CI/CD pipeline integration
release
- Enables isolated agent sessions where unsuccessful experiments can be discarded without disrupting shared code, with successful changes flowing into existing merge requests, pipelines, security checks, and governance controls. Scaling Git for the agentic software factory (2026-10-13) · Oct 2026 · source · release history
Custom Flow network access controls shipped Allows administrators to configure domain allowlists and denylists for remote flows in the Agent Platform.
release
- Admin-defined network access controls allow domain denylists/allowlists for Agent Platform remote flows in Settings 19.0 · May 2026 · source · release history
Advanced project and pipeline data querying shipped Extends the GitLab Query Language to filter and retrieve data across project, pipeline, and job data sources.
release
- Extends GitLab Query Language (GLQL) to query projects, pipelines, and jobs data sources 18.11 · Apr 2026 · source · release history
Unicode and emoji support shipped Adds support for the Unicode 15.1 character set and emoji rendering across the platform.
release
- Adds Unicode 15.1 emoji support 17.7 · Dec 2024 · source · release history
Merge request scheduling shipped Allows developers to schedule future merge requests to be merged automatically at a specified date or time.
release
-
Adds
merge_afterdate field to merge requests to schedule future merges 17.6 · Nov 2024 · source · release history
Task and OKR thread resolution shipped Allow users to mark discussion threads on tasks, objectives, and key results as resolved to streamline planning communication.
release
- Allows resolving threads in tasks, objectives, and key results. 17.3 · Aug 2024 · source · release history
Extended CI/CD rules context control shipped Refine CI/CD job execution logic using the rules:exists keyword with project and ref subkeys to control search scope.
release
-
rules:existsCI/CD keyword acceptsprojectandrefsubkeys to control search context 17.0 · May 2024 · source · release history
FIPS-compliant GitLab Agent installation shipped Install the GitLab Agent for Kubernetes in FIPS 140-2 compliant mode alongside standard Kubernetes components.
Also counts toward: Agent-based deployment, Kubernetes-native deployment
release
-
GitLab agent for Kubernetes can be installed in
FIPSmode alongside Kubernetes components 17.0 · May 2024 · source · release history
CI/CD artifact access control shipped Restrict download permissions for CI/CD job artifacts using the artifacts:access keyword to control audience scope.
release
-
Adds the
artifacts:accesskeyword to control who can download CI/CD job artifacts. 16.11 · Apr 2024 · source · release history
Yarn v4 lockfile scanning shipped suggested Extend dependency scanning capabilities to parse and analyze vulnerabilities in Yarn v4 lockfiles.
Suggested capability: Vulnerability database matching. This is our guess, not confirmed.
release
- Enables dependency scanning for Yarn v4 lockfiles. 16.11 · Apr 2024 · source · release history
Geo-based CI runner traffic offloading shipped Route CI runner execution traffic to secondary Geo sites for self-managed instances to improve latency and distribution.
release
- Offload CI runner traffic to Geo secondary sites for self-managed instances. 16.10 · Mar 2024 · source · release history
CI runner compute usage reporting shipped Export compute minutes consumed by instance runners as CSV data through the Runner Fleet Dashboard for cost tracking.
Also counts toward: CSV data export
release
- Adds CSV export of compute minutes used by instance runners in the Runner Fleet Dashboard 16.8 · Jan 2024 · source · release history
Inline file blame view shipped Show authorship and commit history blame information directly on individual file pages without navigating away.
release
- Adds file blame information view directly on the file page 16.8 · Jan 2024 · source · release history
Issue trend analytics shipped Visualize closed issue counts over time using dedicated analytics report dashboards.
release
- Adds Issue Analytics report visualization for closed issues over time 16.8 · Jan 2024 · source · release history
Scan result branch protection shipped Apply branch modification prevention rules specifically to repositories or paths containing active scan results.
release
- Adds Prevent branch modification setting to scan result policies 16.8 · Jan 2024 · source · release history
CODEOWNERS file validation shipped Checks CODEOWNERS file syntax and format in the web interface to ensure valid reviewer assignment rules before commit.
release
- Adds CODEOWNERS file syntax and format validation in the UI 16.3 · Aug 2023 · source · release history
Upgrade alert notification delivery shipped Provides programmatic delivery of upgrade alerts to external systems via API endpoints.
release
- Adds proper API support to Upgrade Alert notification delivery 15.8.3 · Feb 2023 · source · release history
IP-based rate limiting shipped Restricts cyber tool shell operations by IP address to manage resource consumption and prevent abuse.
release
- Enables rate limiting by IP address on GitLab shell operations 15.8.0 · Jan 2023 · source · release history
Bulk runner deletion shipped GraphQL mutation enabling the bulk deletion of CI runners from the system.
Also counts toward: GraphQL API support
release
-
bulkRunnerDeleteGraphQL mutation for bulk deletion of runners 15.3.0 · Aug 2022 · source · release history
Terraform module package support shipped REST API endpoints for retrieving specific Terraform module versions from the Package registry.
Also counts toward: REST API
release
-
GET /api/v4/packages/terraform/modules/latestandGET /api/v4/packages/terraform/modules/:id/:name/:provider/:versionendpoints for Terraform module versions 15.2.0 · Jul 2022 · source · release history
Namespace CI/CD settings update via GraphQL shipped GraphQL mutation allowing the programmatic updating of CI/CD settings at the namespace level.
Also counts toward: GraphQL API support
release
-
mutation NamespaceCiCdSettingsUpdateallows updating namespace CI/CD settings via GraphQL 15.0.0 · May 2022 · source · release history
Package artifact integrity validation shipped Validation of PyPI file SHA256 values to ensure integrity during import and export operations.
release
- Add validation to pypi file sha256 values to ensure integrity of PyPI artifacts during import/export. 14.9.4 · Apr 2022 · source · release history
Service Ping offline analysis shipped Ability to download the Service Ping payload via the admin area for offline usage and analysis.
release
- Service Ping payload can now be downloaded via the admin area for offline analysis 14.8.0 · Feb 2022 · source · release history
Static site content editing shipped Enables in-browser visual editing of static site content via configuration files, image uploads, and mount definitions for GitLab Pages.
release
-
Adds
.gitlab/static-site-editor.ymlconfig file withstatic_site_generator,image_upload_path, andmountsentries to enable the Static Site Editor feature 13.5.0 · Oct 2020 · source · release history
CI dependency graph visualization shipped Provides a DAG-based visual interface in the CI UI to inspect pipeline job dependencies.
release
- Adds Add DAG visualization MVC to visualize pipeline dependencies using Directed Acyclic Graphs in the CI interface 13.2.0 · Jul 2020 · source · release history
Managed application logs exposure shipped Exposes logs for GitLab-managed applications, such as Helm charts, within the log explorer interface.
release
- Adds Expose gitlab managed apps logs inside log explorer to view logs for GitLab-managed applications like Helm charts 13.2.0 · Jul 2020 · source · release history
Jira project integration shipped Adds the ability to fetch and sync Jira projects within GitLab via GraphQL endpoints.
Also counts toward: GraphQL API support, Ticketing integration
release
-
Introduces
Add a GraphQL endpoint to fetch Jira projects through its REST API.13.1.0 · Jun 2020 · source · release history
Remote mirror configuration via API shipped Provides REST API endpoints to create and remove remote mirrors, enabling programmatic repository replication setup.
Also counts toward: REST API
release
-
New
remote_mirrorsAPI endpoints (GET,POST,DELETE) andremote_mirrorstable columns (keep_divergent_refs) 12.9.0 · Mar 2020 · source · release history
Autocomplete label filtering shipped Restricts autocomplete suggestions in label fields to only applied or relevant labels to streamline metadata entry.
release
- Limit autocomplete menu to applied labels 10.3.0 · Dec 2017 · source · release history
Merge request creation from email shipped Allows developers to create merge requests directly from an email reply without navigating to the web interface.
release
- Allow creation of merge request from email 10.3.0 · Dec 2017 · source · release history
Milestone filtering shipped Allows filtering issues and merge requests by all started milestones for better tracking and filtering.
release
- Allow filtering by all started milestones 9.0.1 · Mar 2017 · source · release history
Instance broadcast messages shipped Allows administrators to distribute system-wide announcements to all cyber tool users.
release
- Add BroadcastMessage API 8.12.0 · Sep 2016 · source · release history
SSH Large File Storage shipped Enables transferring and retrieving large repository files via the SSH protocol.
release
- Add LFS support to SSH 8.12.0 · Sep 2016 · source · release history
External issue tracker integration shipped Enables connecting the cyber tool to external issue tracking systems to synchronize work items and updates.
Also counts toward: Ticketing integration
release
- Add Bugzilla integration. !4930 8.10.0 · Jul 2016 · source · release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
14 commands for GitLab, each with where it came from. This tool has no source analysis yet, so there is no option reference and no captured run beside them.
No command matches.
Screenshots
From the release notes, newest first. Click one to see it full size.Media
Videos from the release notes, newest first. They play right here.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for GitLab, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail GitLab puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Coverage
Missing something? Tell us
What GitLab connects to, runs on and detects, read from its release notes and docs. So far: 4 new integrations, 2 new supported platforms, 1 new detection, 1 updated vulnerability check.
8 changes, tracked since Oct 15, 2026.
-
Oct 282026
new Business Logic Security Analyzer
With missing authorization checks, broken ownership logic, business logic flaws
Our new Business Logic Security Analyzer , the first GitLab capability to support Anthropic's Claude Mythos 5.1, examines how your application enforces its rules: it reads the whole repository and incoming merge requests, infers what each endpoint should enforce, and flags the gaps that pattern-based scanners often miss.
-
Oct 222026
updated Container scanning detection for PHP2Shell (CVE-2026-109618 and CVE-2026-109619)
Container scanning reports vulnerabilities in operating system packages, so it finds PHP installed with apt, apk, or dnf, and it reports the two CVEs once they reach the scanner's vulnerability database.
-
Oct 152026
new External Secrets Operator (Kubernetes) integration
Kubernetes , through External Secrets Operator. ESO re-fetches the secret on a set interval and updates the Kubernetes Secret in place, so a rotated value reaches the cluster without a pipeline run.
-
Oct 152026
new Terraform and OpenTofu data source integration
Terraform and OpenTofu . They read a secret as a data source at plan or apply time and keep credentials out of .tfvars files and CI/CD variables.
-
Oct 152026
new Vault-compatible API for OpenBao and Vault CLIs
OpenBao and Vault CLIs , through the Vault-compatible API. Teams keep their existing scripts and point them at Secrets Manager.
-
Oct 152026
new GitLab Secrets Manager GA on GitLab.com and GitLab Self-Managed (Premium and Ultimate, 19.5)
With GitLab 19.5
It is now generally available in GitLab 19.5 for Premium and Ultimate on GitLab.com and GitLab Self-Managed, with GitLab Dedicated coming soon.
-
Oct 152026
new GitLab MCP server GA — MCP-compatible client support
Adds Claude Code, Claude Desktop, Cursor, GitHub Copilot, OpenAI Codex, Gemini, Kiro, Zed. 8 in all.
You can connect the agents your team already uses by following the MCP server documentation, which includes setup instructions for Claude Code, Claude Desktop, Cursor, GitHub Copilot, OpenAI Codex, Gemini, Kiro, Zed, and other MCP-compatible clients.
-
Oct 152026
new GitLab MCP server available on GitLab.com, GitLab Self-Managed, and GitLab Dedicated
With Free, Premium, Ultimate
The GitLab MCP server is available on the Free, Premium, and Ultimate tiers, on GitLab.com, GitLab Self-Managed, and GitLab Dedicated.
Editors & IDEs 2
Coding agents 4
Chat & assistant apps 1
Model providers & gateways 1
Identity & access 2
Containers & orchestration 2
Other 2
Source control & CI/CD 4
Other 3
Nothing first seen in this window. That doesn't mean GitLab shipped nothing, only that we found no record of it.
How we count
Read from 22 of 241 release notes and docs updates we hold for GitLab. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through GitLab's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
241 entries
No entries match these filters.
- October 202641
- September 202616
- August 202611
- July 20261
- June 20262
- May 20261
- April 20261
- March 20261
- February 20261
- January 20261
- December 20251
- November 20251
- October 20251
- September 20251
- August 20251
- July 20251
- June 20251
- May 20251
- April 20251
- March 20251
- February 20251
- December 20241
- November 20241
- October 20241
- September 20241
- August 20241
- July 202411
- June 20241
- May 20241
- April 20241
- March 20241
- February 20241
- January 20244
- December 20231
- November 20231
- October 20231
- September 20231
- August 20232
- July 20231
- June 20231
- May 20231
- April 20231
- March 20231
- February 20232
- January 20231
- December 20222
- November 20221
- October 20221
- September 20221
- August 20221
- July 20221
- June 20222
- May 20222
- April 20222
- March 20222
- February 20222
- January 20221
- December 20211
- November 20211
- September 20211
- August 20211
- July 20215
- June 20211
- May 20211
- April 20211
- March 20213
- February 20211
- January 20214
- December 20201
- October 20201
- September 20202
- August 20202
- July 20201
- June 20202
- May 20201
- April 20202
- March 20201
- June 20191
- May 20191
- April 20191
- March 20192
- January 20192
- December 20181
- November 20181
- October 20181
- September 20181
- August 20181
- June 20181
- May 20181
- April 20182
- March 20181
- February 20181
- January 20182
- December 20171
- November 20171
- October 20171
- September 20173
- August 20171
- July 20173
- June 20172
- May 20172
- April 20173
- March 20174
- February 20171
- January 20172
- December 20164
- November 20162
- October 20161
- September 20161
- August 20161
- July 20161
- June 20161
- May 20161
- April 20161
- March 20161
- February 20161
- January 20161
- December 20151
- November 20151
- October 20151
- September 20151
Articles
18 articles · updated Nov 4, 2026Where GitLab turns up in what others publish: how-tos, attack reports that name it, and incident write-ups. A row says why it is here and quotes where the article names it; the link goes to the publisher.
Attacks on GitLab 18
-
Send GitLab an email, push to main
This affects all GitLab.com accounts and self-hosted GitLab servers that let users create issues by email.
2 more quotes
Self-hosted GitLab: Maybe.
GitLab Dedicated: No.
-
A Leaked GitLab Issue Email Address Lets Anyone Push Code and Run CI Jobs as You
Anyone who gets it can email a patch that GitLab commits in your name, to any branch you can push to, including main, and can start CI/CD jobs that run as you.
2 more quotes
GitLab shows each user this address behind a button labeled "Email work item to this project." Mail sent to it opens an issue in that project, authored by you.
The string in the middle of the address is a token tied to your account, and GitLab's documentation says it does not expire.
-
GitLab Email Addresses Can Be Weaponized for Supply Chain Attacks
New research from Aikido Security published today examines how a GitLab incoming email address acts as a highly privileged access token that grants broad user rights to an organization's public and private projects.
2 more quotes
GitLab automatically assigns each user of the DevOps platform a private email address to create issues in their software projects; if a user emails the address, a new issue will appear in a project authored by that user.
But GitLab email addresses each contain a non-expiring token that provides broad access to an organization's resources — and not just the project in which an individual user is working.
-
GitLab CVSS 10 File-Read Flaw Draws In-the-Wild Probes After Disclosure
The vulnerability in question is CVE-2026-85706 (CVSS score: 10.0), a path traversal issue in the repository commits API that could allow an unauthenticated user to read arbitrary files from the GitLab server under…
2 more quotes
The problem, per GitLab, stems from "improper path confinement and missing authentication enforcement in the repository commits API." The issue impacts the following versions of GitLab Community Edition (CE) and…
"This is the second instance of a critical severity GitLab vulnerability in recent weeks, following the previous GraphQL code injection ( CVE-2026-19478 ) that was almost immediately actively exploited," Jake Knott,…
Show all 18
-
CISA: Hackers now exploit max severity GitLab flaw in attacks
Cybersecurity and Infrastructure Security Agency (CISA) warned that hackers are now exploiting a maximum-severity GitLab vulnerability in attacks.
2 more quotes
GitLab's DevSecOps platform is used by over 50% of Fortune 100 companies and has over 30 million registered users worldwide.
The security flaw (tracked as CVE-2026-85706 ) stems from missing authentication enforcement and improper path confinement in the repository commits API, and unauthenticated attackers can exploit it to read credentials,…
-
GitLab's critical flaw is already drawing internet-wide probes
GitLab released emergency patches Thursday for two high-severity flaws in its software development platform, one of them holding the highest possible severity score, while a security firm reports that it has already…
2 more quotes
GitLab said its own hosted service already runs the fixed code, and that customers of its single-tenant Dedicated offering are not impacted.
The more serious of the two flaws, tracked as CVE-2026-85706 , sits in the interface that handles repository commits.
-
GitLab urges users to patch max severity path traversal flaw
While GitLab has yet to flag this flaw as exploited in the wild, one day later, cybersecurity company watchTowr reported that attackers have already begun searching for Internet-exposed GitLab servers unpatched against…
2 more quotes
"watchTowr Intel is already observing in-the-wild probes for the latest critical GitLab Path Traversal vulnerability, CVE-2026-85706, which allows attackers to read arbitrary files in a single HTTP request," it warned .
"Based on recent GitLab vulnerabilities, we know the time until indiscriminate exploitation is likely not far away.
-
CVE-2026-85706: Critical GitLab Path Traversal Exploited in the Wild
Overview On September 10, 2026, GitLab published a critical patch release for GitLab Community Edition (CE) and Enterprise Edition (EE).
2 more quotes
The release addresses CVE-2026-85706 , a critical path traversal vulnerability ( CWE-22 ) in the repository commits API with a CVSSv3.1 score of 10.0 .
According to GitLab, improper path confinement and missing authentication enforcement could allow an unauthenticated user to read arbitrary files from an affected GitLab server under certain conditions.
-
Critical GitLab Zero-Click Flaw Poses Mitigation Challenges
GitLab wants organizations running self-managed versions of its software development and DevOps platform to immediately upgrade to new versions released Monday, but patching is not going to eliminate the risk to…
2 more quotes
Two Pre-Auth GitLab Problems Affect Self-Managed Users GitLab has assigned the critical flaw a CVSS score of 9.4 because it requires no authentication or user interaction to exploit, and it has a high impact on data…
The bug affects all GitLab Community Edition/Enterprise Edition (CE/EE) versions from 18.2 before 18.11.11, 19.0 before 19.0.8, 19.1 before 19.1.6, and 19.2 before 19.2.4.
-
Exposed GitLab project email addresses let attackers push code
The addresses are part of a built-in GitLab feature called "Email work item to this project" and contain a long-lived token tied to the developer’s account.
2 more quotes
When an external client sends a message to one of them, GitLab parses it into a project issue or task.
Researchers at application security company Aikido found multiple private GitLab addresses exposed in public documentation and are warning about the associated risk.
-
Gitlab Reconnaissance Introduction
Although Gitlab is not as popular as Github, it’s common to run across it these days.
2 more quotes
Especially after Microsoft acquired Github it seemed more individuals and organizations flocked over to Gitlab.
Let’s assume one has access to a Gitlab Token as a precursor.
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →