Nudge Security
Detect cryptocurrency wallet addresses shared in AI conversations commercialThe section your link pointed to isn't on Nudge Security's page any more, so we've brought you to the top.
Nudge Security is a SaaSSaaSSoftware delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally. security platform that discovers shadow IT assets, manages identity governance, and hardens security posture.
Summary
Nudge Security is a commercial SaaS platform that discovers and inventories SaaS accounts, identities, and AI agents that employees create across an organization, including agents built on platforms like Zapier, Retool, and ChatGPT workspaces that lack public APIs, using a browser extension to fill the gaps. It runs as a hosted service with connected-app integrations across dozens of platforms, feeding findings into ticketing systems like Jira and mapping posture issues to frameworks such as SOC 2SOC 2An auditing framework from the American Institute of CPAs that certifies a service organization's controls around security, availability, and data handling, giving buyers assurance that a vendor meets baseline trust criteria., NIST CSFNIST CSFThe NIST Cybersecurity Framework, a set of outcomes for managing cybersecurity risk. Organizations use it to describe their current posture, priorities and improvement goals., ISOISOA widely adopted international standards body that publishes technical specifications; cyber tools cite ISO standards to signal compliance with recognized benchmarks for quality, security, or interoperability. 27001, and HIPAAHIPAAA US federal law enacted in 1996 that sets privacy and security requirements for protected health information, giving cyber tools a compliance baseline to enforce or audit against.. It's built for security and compliance teams needing visibility into shadow IT and unmanaged AI usage rather than for developers or infrastructure engineers. It sits in the SaaS security posture and identity-access space, and with 27 releases tracked since launching in 2022 and its most recent update 34 days ago, it is under active development.
Nudge Security is a SaaS security platform that discovers shadow IT assets, manages identity governance, and hardens security posture.
How Nudge Security helps
Which AI agents have employees built on platforms that IT never signed off on?
scans platforms without public APIs — Cursor automations, Retool, Zapier Agents, ChatGPT workspace agents, OpenAI Agents Workflows, Atlassian Rovo, Zoom AI Workflows, HyperAgent — via a browser extension and lists each agent found in the identities inventory with its creator and components
Which files and folders in our Google Workspace are visible to people outside the company?
pulls every externally shared file, folder, and Shared Drive across the tenant into one view, filterable by external domain, so shares with a specific outside company can be found and revoked with a scoped confirmation step
Which of our SaaS security findings would fail a SOC 2 or HIPAA audit?
maps every posture finding to the controls it violates across five frameworks and lets findings be filtered down to just the ones tied to a chosen framework, with guided remediation attached to each
How do we get a finding in front of the engineer who owns the account without copying details by hand?
turns any finding into a Jira ticket pre-filled with the finding and its fix, mapped to the right project, work type, priority, and assignee, and keeps an audit trail linking the ticket back to the finding
What proof do we hand an auditor that these issues were tracked and controls were checked?
exports a report scoped to one or all compliance frameworks with the violated controls listed column by column, ready to submit to an auditor or vCISO
Which SaaS accounts and misconfigurations exist on a given platform we already use, like GitLab or LastPass?
connects to the platform as a connected app and centralizes its accounts, activity, and misconfigurations alongside the rest of the SaaS inventory
Languages
Features
Built from Nudge Security's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- Nudge Security covers 1 of the 2 secrets and credential hygiene capabilities we track.
What Nudge Security offers you
- Agent-based deployment2
- Administrative audit log1
- Built-in AI assistant1
- CSV data export1
- Outbound webhooks (the product notifies you)1
- Single sign-on1
- Ticketing integration1
- REST API
No capabilities match.
SaaS and AI Asset Discovery 3 capabilities Nudge Security builds a continuous inventory of every SaaS app, AI tool, and agent employees have introduced across the organisation. It captures who is using what, how apps are connected, and what data they handle.
Connected app integrations shipped Pulls accounts, activity, and configuration data from third-party SaaS and infrastructure platforms into a single unified inventory.
release 133 total
- Adds a Duo Security connected app integration to surface accounts, activity, and misconfigurations from Duo Security inside Nudge Security.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Strengthen your SaaS security posture with our latest connected app for Duo Security · Nov 2026 · source · release history
- Enables the Notion AI agents connected app in Nudge Security to automatically discover and inventory AI agents your team builds on Notion, including creator, components, and risk insights, via the AI Agents tab under Identities.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Discover AI agents built on Notion · Oct 2026 · source · release history
- Adds an in-browser nudge that warns employees on OAuth device code authorization pages for Microsoft, Google, GitHub, GitLab, Salesforce, AWS, Docker, Zoom, Vercel, and OpenAI — every acknowledgment is recorded as a nudge response. changelog · Sep 2026 · source · release history
- Configure detection and enable the device code phishing nudge in Browser Extension Settings. Prevent device code phishing with a new in-browser nudge · Sep 2026 · source · release history
- Enables bulk nudging of employees to migrate credentials into an approved password manager by filtering the accounts inventory by password manager observed at login, multi-selecting accounts, and sending the Use approved password manager nudge — each employee receives one batched nudge listing all their affected… Clean up unapproved password manager use with a single batched nudge · Sep 2026 · source · release history
- Adds a new in-browser nudge that fires on every visit to an OAuth device code authorization page for Microsoft, Google, GitHub, GitLab, Salesforce, AWS, Docker, Zoom, Vercel, and OpenAI, warning employees never to enter a code provided by someone else.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Prevent device code phishing with a new in-browser nudge · Sep 2026 · source · release history
docs
-
By connecting your organization’s Okta account to Nudge Security with a read-only and application administrator API token, you can monitor the SSO enrollment status of your SaaS estate, easily track progress against your organization’s SSO goals, and automatically initiate SSO enrollment workflows directly in Nudge…
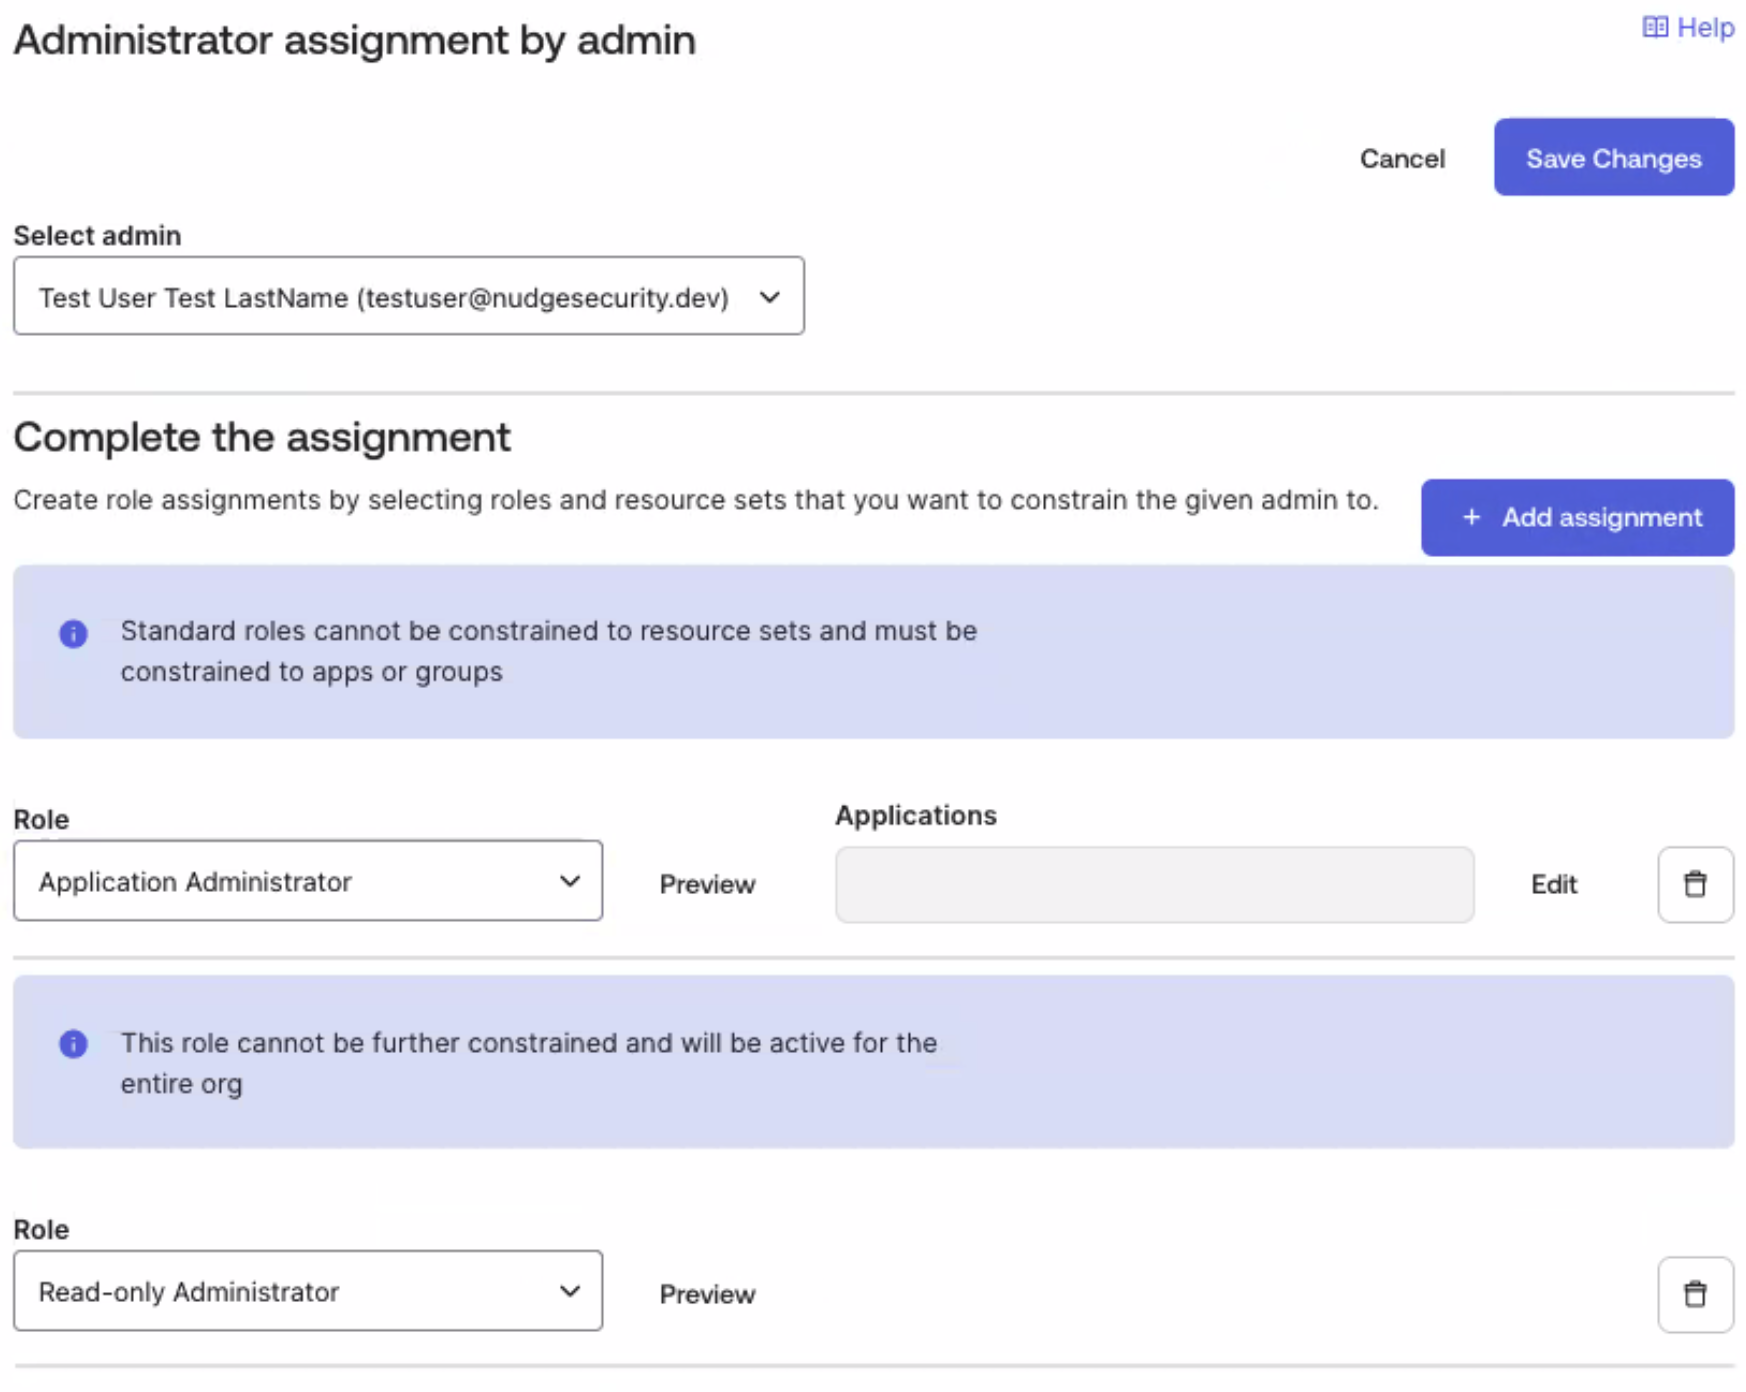 docs update · Oct 2026
· source
-
The Okta connected app uses an API integration between Nudge Security and Okta in order to share information and perform certain actions between the two services. To enable the Okta connected app, you'll need to create an API token in Okta and configure it in Nudge Security.
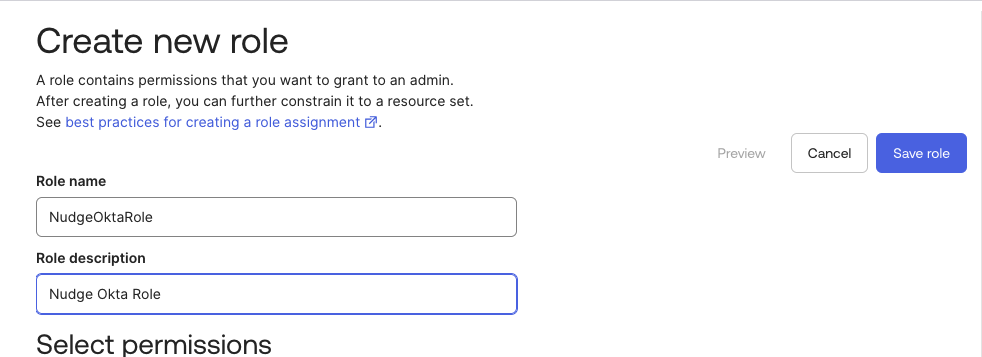 docs update · Oct 2026
· source
- Updated today User.Read, profile, openid, email Basic scopes for user identification on initial authentication with the app Basic scopes required for user identification on initial authentication with the app Scoping Microsoft Entra ID Analysis to a Specific Set of Users seen Aug 2026 · source
example 7 total
-
Remediate shadow password manager use in bulk — send each employee a single nudge listing every account where a non-approved password manager was observed at login.
In the Nudge Security console, go to Accounts Inventory > Filter by 'Password Manager' > select any manager not marked approved > multi-select matching accounts > Send Nudge > 'Use approved password…changelog · Sep 2026 · source -
Enable device code phishing protection so employees are warned the moment they land on an OAuth device code authorization page.
In the Nudge Security console, go to the device code phishing detection settings, enable detection, and turn on the in-browser nudge to activate warnings across Microsoft, Google, GitHub, GitLab,…changelog · Sep 2026 · source -
Enable the device code phishing protection for your organization by configuring the browser extension settings.
In Nudge Security, go to Browser Extension Settings and enable the nudge for device code pages.Prevent device code phishing with a new in-browser nudge · Sep 2026 · source -
Enable the device code phishing nudge so employees are warned in real time whenever they land on an OAuth device code authorization page.
In the Nudge Security console, go to Browser Extension Settings, locate the device code phishing detection option, and turn on the nudge.Prevent device code phishing with a new in-browser nudge · Sep 2026 · source -
Clean up shadow IT by identifying all accounts using unapproved password managers and sending a consolidated migration nudge to affected users.
In the console, go to Accounts Inventory, filter by 'password manager observed at login' excluding approved providers, multi-select the results, and send the "Use approved password manager" nudge.Clean up unapproved password manager use with a single batched nudge · Sep 2026 · source -
Enable the GitLab connected app in Nudge Security to surface account misconfigurations and activity across your GitLab organization.
In the Nudge Security console, go to Integrations, search for GitLab, and follow the connection prompts to authorize and link your GitLab organization.Strengthen your SaaS security posture with our latest connected apps for GitLab, Informatica, and Logz.io · seen Jul 2026 · source
AI agent discovery and inventory shipped Discovers and inventories AI agents employees have built across platforms, showing the creator, components used, and associated risks.
release 51 total
- Nudge Security now discovers shadow AI agents through browser activity in addition to existing API integrations, covering platforms whose APIs are limited or unavailable to security teams. announced · Nov 2026 · source · release history
-
Access the full AI agent inventory at
Identities > AI agents, where each agent shows its creator, platform, integrations, permissions, and approval status regardless of which discovery channel found it.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Discover and govern AI agents across 23 agentic platforms · Nov 2026 · source · release history - Browser-based discovery now covers Cursor automations, Retool, Zapier Agents, ChatGPT workspace agents, OpenAI Agent Workflows, Atlassian Rovo (Jira, Bitbucket), Zoom AI Workflows, HyperAgent, HubSpot agents, Datadog, and Amazon — bringing total platform coverage to 23 across both discovery channels. announced · Nov 2026 · source · release history
-
AI agents are accessible via
Automations > AI Agentsin the Nudge Security console. Address sprawling OAuth and browser extension risk with Nudge Security AI agents, now live · Sep 2026 · source · release history - Discovers AI agents built on Datadog and HubSpot as part of the AI agent discovery research preview, surfaced through the browser extension. changelog · Aug 2026 · source · release history
- Discovers AI agents your team builds on Datadog and HubSpot through browser-based detection, flowing each agent into the AI agents inventory under Identities with creator, components, and risk insights. Discover AI agents built on Datadog and HubSpot · seen Aug 2026 · source · release history
docs
- August 19, 2026 Discover AI agents built on Datadog and HubSpot Nudge Security now discovers AI agents your team builds on Datadog and HubSpot, right from the browser. This is available as part of the AI agent discovery research preview. changelog · Aug 2026 · source
example 9 total
-
Activate browser-based agent discovery to surface shadow AI agents your employees are building in tools like Cursor or Zapier Agents that have no enterprise API.
In the Nudge Security browser extension settings, toggle 'AI agent discovery' on. Agents will start appearing in Identities > AI agents inventory as employees view or create them.announced · Nov 2026 · source -
Enable Notion AI agent discovery during the research preview to surface AI agents your team has built on Notion.
In Nudge Security, go to the AI Agents tab under Identities, then enable the 'Notion AI agents' connected app. If not yet in the research preview, request access from the same tab.changelog · Oct 2026 · source -
Enable Notion AI agent discovery so every agent your team builds surfaces automatically in the AI agents inventory with creator, components, and risk insights.
In Nudge Security, go to Identities > AI Agents tab, then enable the 'Notion AI agents' connected app to start ingesting agents into your inventory.Discover AI agents built on Notion · Oct 2026 · source -
Enable browser-based AI agent discovery to surface Datadog and HubSpot agents your team has built.
In the Nudge Security browser extension, go to Settings and turn on browser-based agent discovery.changelog · Aug 2026 · source -
Enable browser-based AI agent discovery so Datadog- and HubSpot-built agents automatically appear in your inventory.
In the Nudge Security browser extension, go to Settings and turn on 'browser-based agent discovery'.Discover AI agents built on Datadog and HubSpot · seen Aug 2026 · source -
Enable browser-based agent discovery to populate your AI agents inventory with Amazon Quick agents your team builds.
In the console, go to Browser Extension Settings and enable browser-based agent discovery, then view discovered agents under Identities > AI Agents.changelog · seen Jul 2026 · source
App business criticality and data type classification shipped Automatically classifies each app by business criticality and infers the types of data it handles, with customisable sensitivity tiers.
release 17 total
- Adds adaptive monitoring that automatically begins surfacing additional findings — such as password reuse or weak authentication — when an app is marked business-critical. announced · seen Sep 2026 · source · release history
- Adds automatic app criticality tiering that classifies every application by breadth of use and data sensitivity using a proprietary AI model identifying up to 29 distinct data types.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · seen Sep 2026 · source · release history
-
Adds automated business criticality tiering for every discovered SaaS and AI app, assigning each a
critical,high,medium, orlowtier based on organizational spread and inferred data sensitivity.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Sep 2026 · source · release history - Adds Automatic app tiering to prioritize highest-impact apps based on adoption and up to 29 inferred data types Respond dynamically to evolving SaaS and AI risks with adaptive risk management · Sep 2026 · source · release history
- Introduces automatic app tiering that prioritizes apps based on organizational adoption and the sensitivity of up to 29 inferred data types, with no manual entry required. Respond dynamically to evolving SaaS and AI risks with adaptive risk management · Sep 2026 · source · release history
- Uses a proprietary AI model to infer up to 29 data types each app typically handles, mapping them to sensitivity tiers that customers can customize to align with internal data governance models. announced · Sep 2026 · source · release history
example
-
Promote a newly-deployed app to business-critical so Nudge immediately begins tracking additional findings like password reuse and weak authentication.
In the Nudge Security console, open the application's detail page, locate the criticality tier selector, and set it to 'Business Critical' — Nudge will automatically begin surfacing additional…announced · seen Sep 2026 · source -
Focus security posture reviews on apps that handle sensitive data by filtering the inventory by data type and criticality tier.
In the app inventory, use the Data Types filter to select a sensitive category (e.g., financial data) and the Business Criticality filter set to Critical or High to surface the apps warranting…changelog · seen Jul 2026 · source -
Customize which data types are considered high-sensitivity to align automatic criticality tiers with your organization's governance model.
In the console, go to Settings > Risk and adjust the data sensitivity tier assignments to match your organization's data governance model.Prioritize your SaaS and AI inventory automatically with data types and business criticality tiers, now in open beta · seen Jul 2026 · source
Risk Assessment and Scoring 4 capabilities The cyber tool evaluates the risk posed by every discovered vendor, OAuth connection, and browser extension. Scores update automatically as new signals emerge, giving teams a current picture of exposure.
SaaS and AI vendor risk scoring shipped Assigns inherent and residual risk scores to every SaaS and AI vendor, recalculated automatically as risk signals change.
release 22 total
- Introduces a dynamic risk score per app calculated from more than 30 internal and external factors — including OAuth grants and scopes, MCP connections, AI agent permissions, authentication methods, SSO coverage, MFA enrollment, security posture findings, stale accounts, and vendor breach/supply-chain intelligence —… announced · Sep 2026 · source · release history
- Adds continuous dynamic risk scoring built from more than 30 factors — combining vendor external security posture with internal usage signals such as OAuth grant staleness, MCP connections, SSO vs. announced · seen Sep 2026 · source · release history
- Adds always-on dynamic app risk scores driven by 30 internal and external factors, updating automatically without vendor participation. Respond dynamically to evolving SaaS and AI risks with adaptive risk management · Sep 2026 · source · release history
- Adds a Risk tab per app surfacing a ranked breakdown of control gaps and the factors driving each risk score, updated continuously as internal usage and vendor conditions change. announced · Sep 2026 · source · release history
- Enables adaptive, policy-driven controls that automatically expand security posture monitoring, strengthen authentication requirements, or route remediation to app owners, administrators, or users as an app's criticality or risk score shifts. announced · Sep 2026 · source · release history
- Introduces inherent and residual risk scores (Low/Medium/High/Critical) for every SaaS and AI vendor, with transparent factor breakdowns covering vendor security posture, internal deployment risk, and compensating controls — now in open beta. changelog · seen Jul 2026 · source · release history
example
-
Review concentrated SaaS and AI risk exposure across your estate and monitor how scores shift over time as vendor conditions change.
In the Nudge Security console, go to Dashboards > Risk to view app tiers, dynamic risk scores, and exposure trends across your SaaS and AI portfolio.Respond dynamically to evolving SaaS and AI risks with adaptive risk management · Sep 2026 · source -
Review the ranked control gaps driving risk for a specific app so you know what to remediate first before a vendor posture change escalates exposure.
In the Nudge Security console, navigate to the app's detail page and select the 'Risk' tab to see a ranked breakdown of control gaps and the factors contributing to its current dynamic risk score.announced · Sep 2026 · source -
Identify your highest-risk AI vendors by combining residual risk score with recommended remediation actions.
In the app inventory, filter by Risk Score = Critical or High, then open any app overview and click the Risk tab to view the factor breakdown and ranked recommended actions.changelog · seen Jul 2026 · source -
Review the full risk breakdown and recommended remediations for a specific app to decide what to fix next.
In the Nudge Security console, open your App Inventory, select any SaaS or AI app, then click the Risk tab to view its inherent and residual risk scores, contributing risk factors, and recommended…Know your real vendor risk with inherent and residual risk scores, now in open beta · seen Jul 2026 · source -
Filter your entire app inventory by risk level to quickly surface Critical or High residual-risk vendors across the organization.
In the Nudge Security console, go to App Inventory and use the risk score filter to narrow the view to Critical or High residual risk apps.Know your real vendor risk with inherent and residual risk scores, now in open beta · seen Jul 2026 · source
OAuth grant risk analysis and remediation shipped Reviews OAuth grants across the estate, flags overly permissive or high-risk ones, and supports revocation or owner notification.
Also counts toward: Agent-based deployment, Built-in AI assistant
release 15 total
- Adds the OAuth Grant Risk Analyst AI agent, accessible via Automations > AI Agents, which reviews new OAuth grants as they are discovered, revokes overly permissive or high-risk ones automatically, or nudges the OAuth grantor to remove access, with human-in-the-loop oversight.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ changelog · Oct 2026 · source · release history
- Adds the OAuth Grant Risk Analyst AI agent, which reviews new OAuth grants as they are discovered, automatically revokes overly permissive or high-risk access, or nudges the OAuth grantor to remove it, with human-in-the-loop oversight.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Address sprawling OAuth and browser extension risk with Nudge Security AI agents, now live · Sep 2026 · source · release history
- Introduces the OAuth Risk Analyst AI agent to trigger and conduct reviews of high-risk OAuth grants automatically as risk scores change. announced · Sep 2026 · source · release history
- Deploys the OAuth Grant Risk Analyst to review new integration OAuth grants and resolve overly permissive ones via automatic revocation or nudging Address sprawling OAuth and browser extension risk with Nudge Security AI agents, now live · Sep 2026 · source · release history
- New OAuth Grant Risk Analyst AI agent reviews newly discovered OAuth grants, flags overly permissive or high-risk ones, and resolves them by automatically revoking access or nudging the grantor — with human-in-the-loop oversight. Address sprawling OAuth and browser extension risk with new Nudge Security AI agents · seen Jul 2026 · source · release history
- Adds real-time alerts when employees interact with not permitted apps (e.g., file uploads or OAuth grants) detected from the browser extension Address risky behavior with real-time notifications for activity in not-permitted apps · Sep 2025 · source · release history
docs
- Using the OAuth Analyst Agent How to turn on the OAuth Analyst Agent, configure what it does with each verdict, and act on what it finds. seen Oct 2026 · source
- September 30, 2026 Address sprawling OAuth and browser extension risk with Nudge Security AI agents, now live OAuth Grants Nudge Security's AI agents are now live, so you can tackle sprawling OAuth and browser extension risk at scale. changelog · Oct 2026 · source
- 27 articles Risk Agents Let AI agents review risky OAuth grants and browser extensions for you, and decide how much they act on their own. Using the OAuth Analyst Agent How to turn on the OAuth Analyst Agent, configure what it does with each verdict, and act on what it finds. docs update · Oct 2026 · source
example
-
Activate the OAuth Grant Risk Analyst to automatically handle newly discovered high-risk OAuth grants without manual triage.
In the Nudge Security console, go to Automations > AI Agents and enable the OAuth Grant Risk Analyst.changelog · Oct 2026 · source -
Enable the OAuth Grant Risk Analyst to automatically revoke high-risk OAuth grants as Nudge Security discovers them, reducing manual triage.
In the Nudge Security console, go to Automations > AI Agents, select 'OAuth Grant Risk Analyst', configure your revocation and nudge preferences, and activate the agent.changelog · Oct 2026 · source -
Enable the OAuth Grant Risk Analyst to automatically revoke high-risk OAuth grants as they appear, without manual review for every new integration.
In the console, go to Automations > AI Agents, select 'OAuth Grant Risk Analyst', configure human-in-the-loop approval settings, and activate the agent.Address sprawling OAuth and browser extension risk with Nudge Security AI agents, now live · Sep 2026 · source -
Access the new AI agent controls to start managing OAuth and extension risks.
Automations > AI AgentsAddress sprawling OAuth and browser extension risk with Nudge Security AI agents, now live · Sep 2026 · source -
Enable and authorize the OAuth Grant Risk Analyst agent to automatically review and act on new OAuth grants as they appear in your environment.
In the Nudge Security console, go to Automations > Agents, select 'OAuth Grant Risk Analyst', and authorize it to permit, justify, or revoke grants on new integration discoveries.announced · Sep 2026 · source
AI conversation sensitive data detection shipped Monitors AI platform conversations via the browser extension and flags secrets, PII, financial, or health data employees have entered.
release 13 total
- Enable cryptocurrency wallet address detection in AI conversation monitoring via Browser Extension Settings to catch when employees share crypto data with AI tools.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Detect cryptocurrency wallet addresses shared in AI conversations · Nov 2026 · source · release history
-
New in-browser nudge (
Settings > In-browser nudges) intercepts sensitive data (PII, secrets, financial info) detected in AI-tool conversations, shows the employee exactly what was found, and offers one-click redaction; optional enforcement mode blocks sending until sensitive data is redacted. changelog · Aug 2026 · source · release history -
Adds in-browser nudges via the browser extension that detect PII, secrets, or financial info typed into AI conversations and prompt employees to redact in one click or justify sending — configurable at
Settings > In-browser nudges. Nudge employees in the browser before they share sensitive data in AI conversations · seen Aug 2026 · source · release history -
Adds optional enforcement mode (configurable at
Settings > In-browser nudges) that makes redaction the only way to send, preventing unredacted sensitive data from leaving the browser. Nudge employees in the browser before they share sensitive data in AI conversations · seen Aug 2026 · source · release history -
Adds
Settings > In-browser nudgesnavigation path to enable sensitive data detection in browser extensions Nudge employees in the browser before they share sensitive data in AI conversations · Aug 2026 · source · release history - Adds enforcement mode to the in-browser nudge configuration, making redaction mandatory before sending Nudge employees in the browser before they share sensitive data in AI conversations · Aug 2026 · source · release history
docs
- July 29, 2026 Detect sensitive data shared in Amazon Quick Suite AI conversation monitoring now detects sensitive data shared in Amazon Quick Suite, Amazon's agentic AI platform. When someone enters secrets, PII, financial data, or health data into an Amazon Quick chat, Nudge Security flags it. changelog · seen Jul 2026 · source
example
-
Turn on cryptocurrency detection so your team is alerted when employees paste wallet addresses or related crypto identifiers into AI tools.
In Nudge Security, go to Browser Extension Settings and enable cryptocurrency detection.Detect cryptocurrency wallet addresses shared in AI conversations · Nov 2026 · source -
Prevent unredacted PII or secrets from reaching AI tools across your org by enabling enforcement mode for in-browser nudges.
In the Nudge Security console, go to Settings > In-browser nudges, enable sensitive data nudges, then turn on 'enforce redaction' so employees cannot send AI conversations containing detected…changelog · Aug 2026 · source -
Enable sensitive data nudges with mandatory redaction so employees can never paste unredacted PII or secrets into AI tools.
In the console, go to Settings > In-browser nudges, enable 'sensitive data nudges', then turn on enforcement so redaction is required before sending.Nudge employees in the browser before they share sensitive data in AI conversations · seen Aug 2026 · source -
Turn on AI conversation monitoring to flag sensitive data entered into Amazon Quick Suite chats.
In the console, go to Browser Extension Settings and configure AI conversation monitoring detection.changelog · seen Jul 2026 · source -
Enable detection of sensitive data shared in Amazon Quick Suite for your organization.
In the Nudge Security console, go to Browser Extension Settings and configure AI conversation monitoring to include Amazon Quick Suite.Detect sensitive data shared in Amazon Quick Suite · seen Jul 2026 · source
Browser extension risk analysis shipped Inspects browser extension metadata to identify malicious or compromised extensions and supports disable and uninstall workflows.
Also counts toward: Agent-based deployment
release 11 total
- Adds the Browser Extension Risk Analyst AI agent, accessible via Automations > AI Agents, which inspects browser extension artifacts and metadata to flag malicious, compromised, or misrepresented extensions and orchestrates disable and uninstall workflows. changelog · Oct 2026 · source · release history
- Deploys the Browser Extension Risk Analyst to inspect installed third-party browser extension artifacts and metadata, flagging malicious or risky extensions Address sprawling OAuth and browser extension risk with Nudge Security AI agents, now live · Sep 2026 · source · release history
- Adds the Browser Extension Risk Analyst AI agent, which inspects artifacts and metadata behind installed browser extensions, flags malicious, compromised, or misrepresented extensions, and orchestrates disable and uninstall workflows. Address sprawling OAuth and browser extension risk with Nudge Security AI agents, now live · Sep 2026 · source · release history
- New Browser Extension Risk Analyst AI agent inspects installed browser extension artifacts and metadata, flags malicious, compromised, or misrepresented extensions, and orchestrates disable and uninstall workflows. Address sprawling OAuth and browser extension risk with new Nudge Security AI agents · seen Jul 2026 · source · release history
- Enables identification of high-risk and outdated browser extensions across supported browsers. Inventory browser extensions installed across your organization · Dec 2025 · source · release history
- Adds the Browser Extensions tab within the App-to-App Integrations section of the product to view detailed insights into extension landscape at user and extension level. Inventory browser extensions installed across your organization · Dec 2025 · source · release history
docs
- 14 articles Removing the Nudge Security browser extension from managed devices How to remove an MDM-deployed Nudge Security browser extension, with links to browser and MDM vendor documentation. seen Oct 2026 · source
example
-
Activate the Browser Extension Risk Analyst to continuously inspect employee-installed extensions and trigger disable/uninstall workflows for risky ones.
In the Nudge Security console, go to Automations > AI Agents and enable the Browser Extension Risk Analyst.changelog · Oct 2026 · source -
Deploy the Browser Extension Risk Analyst to continuously inspect employee-installed extensions and trigger disable/uninstall workflows for flagged ones.
In the Nudge Security console, go to Automations > AI Agents, select 'Browser Extension Risk Analyst', set your risk thresholds and remediation actions, and activate the agent.changelog · Oct 2026 · source -
Enable the Browser Extension Risk Analyst agent to automatically disable and block malicious or compromised browser extensions across your fleet.
In the Nudge Security console, go to Automations > Agents, select 'Browser Extension Risk Analyst', and authorize it to disable and block extensions rated 'malicious' or 'compromised'.announced · Sep 2026 · source -
Deploy the Browser Extension Risk Analyst to continuously inspect installed extensions across your organization and trigger disable or uninstall workflows for malicious or compromised ones.
In the console, go to Automations > AI Agents, select 'Browser Extension Risk Analyst', and activate the agent to begin scanning installed browser extensions and orchestrating remediation.Address sprawling OAuth and browser extension risk with Nudge Security AI agents, now live · Sep 2026 · source
Remediation and Access Control 2 capabilities Nudge Security provides direct controls to tighten or revoke access rather than just surfacing findings. Teams can act on risky sharing, OAuth grants, and login paths from within the cyber tool.
SSO login enforcement shipped Disables alternative sign-in methods org-wide so that all logins flow through the configured identity provider and its access controls.
Shared capability: Single sign-on
Also counts toward: Single sign-on
release
- Enables organizations to enforce SSO-only login, disabling Google and Microsoft sign-in methods so all authentication routes through the configured IdP (e.g., Okta) with its MFA and conditional access controls. changelog · seen Jul 2026 · source · release history
- Adds SSO login enforcement that disables alternative sign-in methods (Sign in with Google, Sign in with Microsoft) org-wide, routing all logins through your configured IdP (e.g., Okta) to inherit its MFA, conditional access, and deprovisioning controls. Enforce SSO login for Nudge Security · seen Jul 2026 · source · release history
- Enables organization-level enforcement of SSO login via a new login restrictions toggle in the Organization settings page Enforce SSO login for Nudge Security · Jul 2026 · source · release history
- Adds authentication method details (SSO providers, OAuth, username/password) and last activity to each application account insight view Additional insight into authentication methods and MFA · Oct 2023 · source · release history
- Adds the ability to filter application accounts by authentication type in the UI Additional insight into authentication methods and MFA · Oct 2023 · source · release history
docs
-
Requirements Admin access to an Okta organization Supported Features Service Provider (SP)
-InitiatedAuthentication (SSO) Flow - This authentication flow occurs when the user attempts to log in to the application from Nudge Security. docs update · Oct 2026
· source
-
This guide walks you through creating an app registration in Microsoft Entra ID (formerly Azure Active Directory) so your team can sign in to Nudge Security with their Microsoft credentials using OpenID Connect (OIDC). When you're done, you'll send three values to Nudge Security.
 docs update · Oct 2026
· source
- 9 articles Configure single sign-on with Microsoft Entra ID Set up a Microsoft Entra ID app registration so your team can sign in to Nudge Security with their Microsoft credentials. docs update · Oct 2026 · source
- September 8, 2026 Deploy the Nudge Security browser extension on Safari for more complete SaaS & AI visibility and enforcement SaaS Discovery You can now deploy the Nudge Security browser extension on Safari, extending coverage to the default browser on every company Mac. changelog · Sep 2026 · source
Google Drive external share visibility and remediation shipped Surfaces all externally shared Google Drive files and folders in one view and provides per-item controls to tighten or revoke permissions.
release 7 total
- Adds filtering of security posture findings to surface them only for Critical and High tier apps Prioritize your SaaS and AI inventory automatically with data types and business criticality tiers, now in open beta · Jul 2026 · source · release history
- Enables filtering external shares by domain to see everything shared with a specific external company for targeted cleanup. Discover and revoke risky external file shares in Google Drive · seen Jul 2026 · source · release history
- New Google Drive integration surfaces every externally shared file, folder, and Shared Drive across a Google Workspace tenant in a single view. Discover and revoke risky external file shares in Google Drive · seen Jul 2026 · source · release history
- Per-item access controls let administrators tighten or revoke external share permissions with a confirmation step that details scope before changes are applied. Discover and revoke risky external file shares in Google Drive · seen Jul 2026 · source · release history
- Enables at-a-glance view of SaaS service disruptions for security and IT teams Monitor app outages with new app health statuses · Dec 2023 · source · release history
- Adds new app health statuses that show the operational state of SaaS applications across your organization Monitor app outages with new app health statuses · Dec 2023 · source · release history
example
-
Review all externally shared files and Shared Drives across your Google Workspace tenant to identify and revoke risky shares.
In the Nudge Security console, go to Inventory > External File Shares.Discover and revoke risky external file shares in Google Drive · seen Jul 2026 · source -
Navigate the new UI view to identify risky external shares in Google Workspace.
Inventory > External File SharesDiscover and revoke risky external file shares in Google Drive · Jul 2026 · source
Compliance and Audit Reporting 2 capabilities The cyber tool maps findings to major compliance frameworks and produces audit-ready exports. Every administrative action is also logged to support evidence collection.
Administrative audit log shipped Records every administrative action taken within the cyber tool and exports the log as CSV for compliance evidence.
Also counts toward: Administrative audit log, CSV data export
release 9 total
- Records every acknowledgment as a nudge response and allows configuration in Browser Extension Settings Prevent device code phishing with a new in-browser nudge · Sep 2026 · source · release history
- Exports a complete admin activity log as CSV, capturing OAuth revocations, role changes, field/setting updates, and app connect/disconnect events (Settings > Audit event). changelog · seen Jul 2026 · source · release history
- New audit log records every administrative action — OAuth revocations (with reason), role changes, field and setting updates, and app connect/disconnect events — exportable as CSV for SOC 2 and compliance evidence. Export a complete log of admin activity · seen Jul 2026 · source · release history
- Exports Nudge history to CSV format Export your Nudge history to CSV · Sep 2025 · source · release history
- Enables export of Nudge history to track trends and support audits Export your Nudge history to CSV · Sep 2025 · source · release history
- Adds Microsoft Teams integration to deliver nudges and receive notifications Deliver nudges and receive notification on Microsoft Teams with new integration · Sep 2025 · source · release history
docs
-
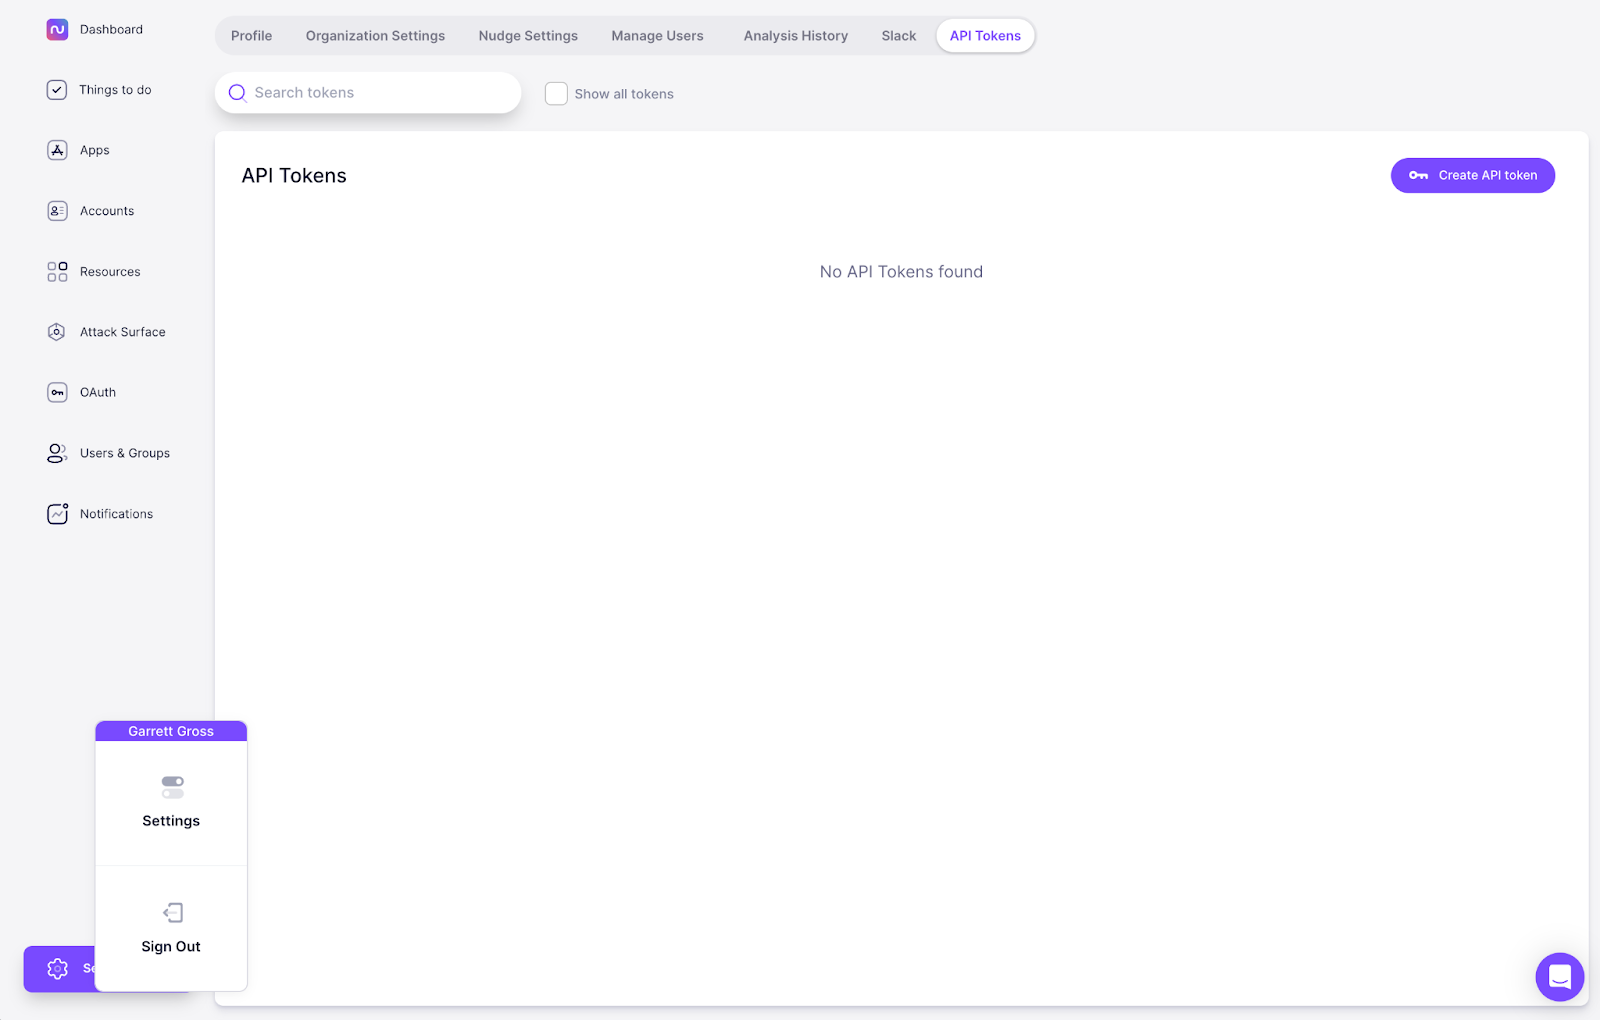
Create and manage API keys Note: You will need to have the administrator role in order to create API keys in Nudge Security. Setting up an API key in Nudge Security is easy and is done from the UI Under Settings , navigate to API Tokens. Click Create API Token.
 docs update · Oct 2026
· source
- July 22, 2026 Export a complete log of admin activity You can now export a log of every administrative action taken in Nudge Security, so you have a clear record of who changed what and when. changelog · seen Jul 2026 · source
example
-
Audit who revoked OAuth grants or changed roles over a given period — useful after a security incident or for compliance reviews.
In the console, go to Settings > Audit event, filter events by date or action type, then click Export to download the log as a CSV.changelog · seen Jul 2026 · source -
Pull a CSV of all admin actions for a SOC 2 audit or incident investigation.
In the console, go to Settings > Audit event, review the log of administrative actions, then click Export to download as CSV.Export a complete log of admin activity · seen Jul 2026 · source
Compliance framework mapping and audit reporting shipped Maps posture findings to SOC 2, NIST CSF, ISO 27001, HIPAA, and OWASP Agentic AI controls and exports audit-ready reports filtered by framework.
release 10 total
- Surfaces security posture findings selectively for Critical and High tier apps, reducing noise for lower-risk apps. Prioritize your SaaS and AI inventory automatically with data types and business criticality tiers, now in open beta · seen Jul 2026 · source · release history
- Adds compliance framework filtering on the Security Posture Findings view to surface every control violation across a SaaS estate at a glance. Security posture findings now mapped to compliance frameworks · seen Jul 2026 · source · release history
- Exports audit-ready reports with compliance framework and control columns included. Security posture findings now mapped to compliance frameworks · seen Jul 2026 · source · release history
- Maps security posture findings to five compliance frameworks: SOC 2, NIST CSF 2.0, ISO 27001, HIPAA, and OWASP Top 10 Agentic AI Security. Security posture findings now mapped to compliance frameworks · seen Jul 2026 · source · release history
- Enables drill-down into any finding to view the specific controls it violates alongside guided remediation in the same panel. Security posture findings now mapped to compliance frameworks · seen Jul 2026 · source · release history
- Adds filtering of security posture findings by specific compliance framework Security posture findings now mapped to compliance frameworks · Jun 2026 · source · release history
example
-
Quickly scope your SOC 2 audit prep by filtering all posture findings to only those that violate SOC 2 controls.
In the console, go to Security Posture > Findings, then use the compliance framework filter to select SOC 2. Review each listed finding and follow guided remediation from the detail panel.Security posture findings now mapped to compliance frameworks · seen Jul 2026 · source -
Generate an audit-ready export covering all compliance frameworks for submission to an auditor or vCISO.
In the console, go to Security Posture > Findings, apply any desired framework filters, then select Export to download a report with compliance framework and control columns included.Security posture findings now mapped to compliance frameworks · seen Jul 2026 · source
Workflow and Ticketing Integrations 1 capability Nudge Security connects findings directly to existing engineering and operations workflows. Jira tickets are created pre-filled with context so remediation work enters the team's normal queue without manual transcription.
Finding remediation ticketing integrations shipped Creates Jira tickets directly from findings, pre-filled with details and fix recommendations, and maintains a linked audit trail between findings and issues.
previously: Jira integration for finding remediation
Also counts toward: Ticketing integration
release 9 total
- Maintains a linked audit trail between Nudge Security findings and their associated Jira issues. Create Jira tickets from your Nudge Security findings · seen Jul 2026 · source · release history
- New Jira integration creates tickets directly from any finding, pre-filled with finding details and fix recommendations. Create Jira tickets from your Nudge Security findings · seen Jul 2026 · source · release history
- Supports mapping tickets to Jira project, work type, priority, assignee, and reporter during creation. Create Jira tickets from your Nudge Security findings · seen Jul 2026 · source · release history
- Findings can now create pre-filled Jira tickets mapped to project, work type, priority, assignee, and reporter Create Jira tickets from your Nudge Security findings · Jun 2026 · source · release history
- Admins can connect Jira by navigating to Settings > Ticketing to enable ticket creation from findings Create Jira tickets from your Nudge Security findings · Jun 2026 · source · release history
- Adds a new Tines story integration to create Jira tickets for Nudge Security SaaS security posture findings Create Jira tickets for SaaS security posture findings with Tines · Nov 2024 · source · release history
docs
- This article covers connecting ServiceNow, mapping your fields, and creating your first ticket. Before you start You'll need admin access in Nudge Security to set up the connection. You'll need your ServiceNow instance URL You'll need a ServiceNow account with permission to create records in the table you plan to use. docs update · Oct 2026 · source
-
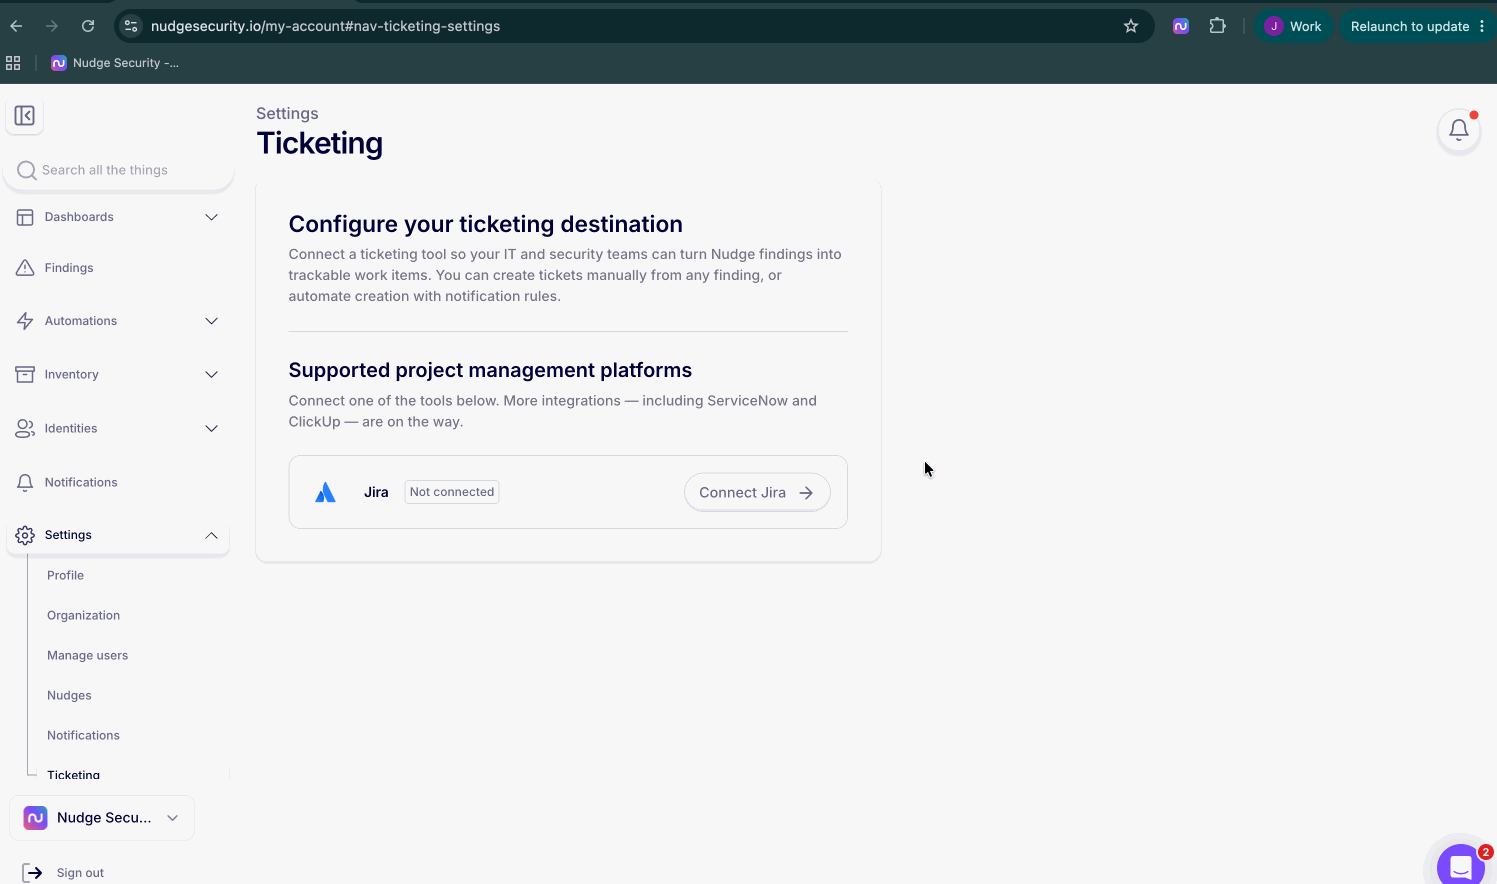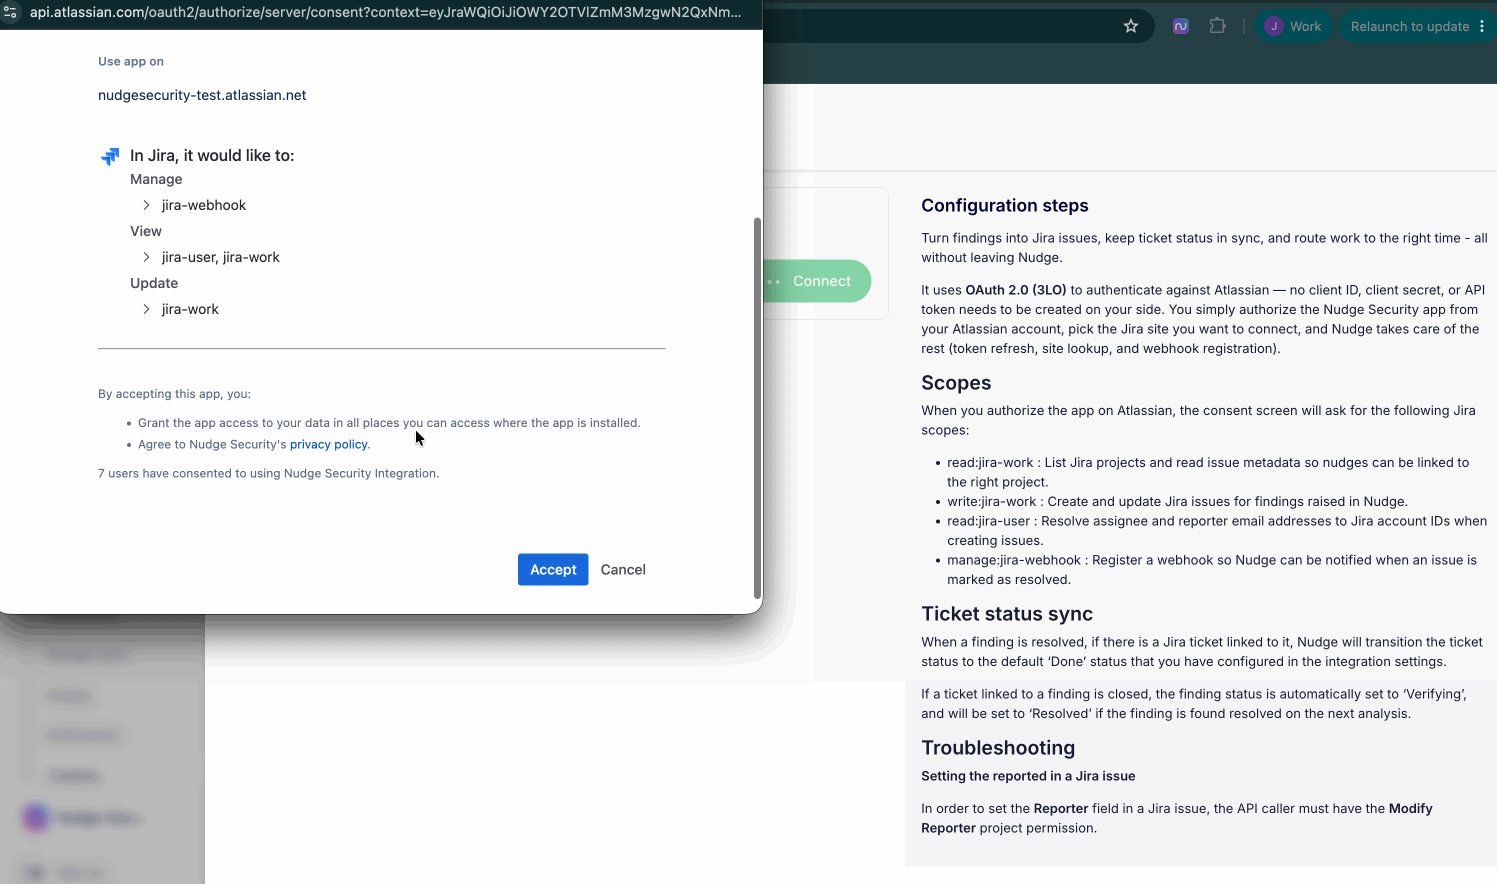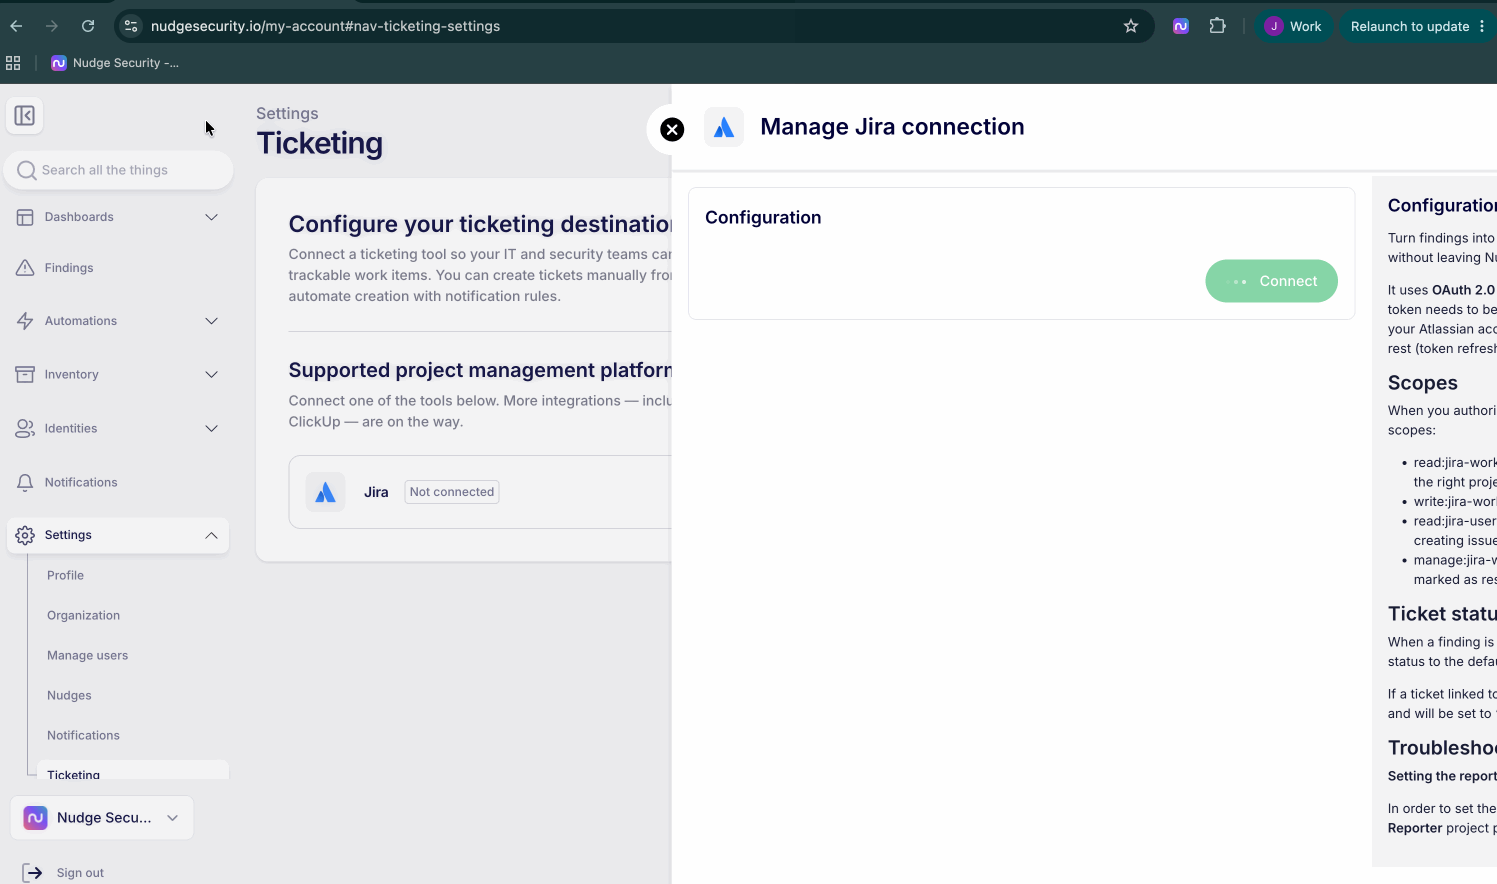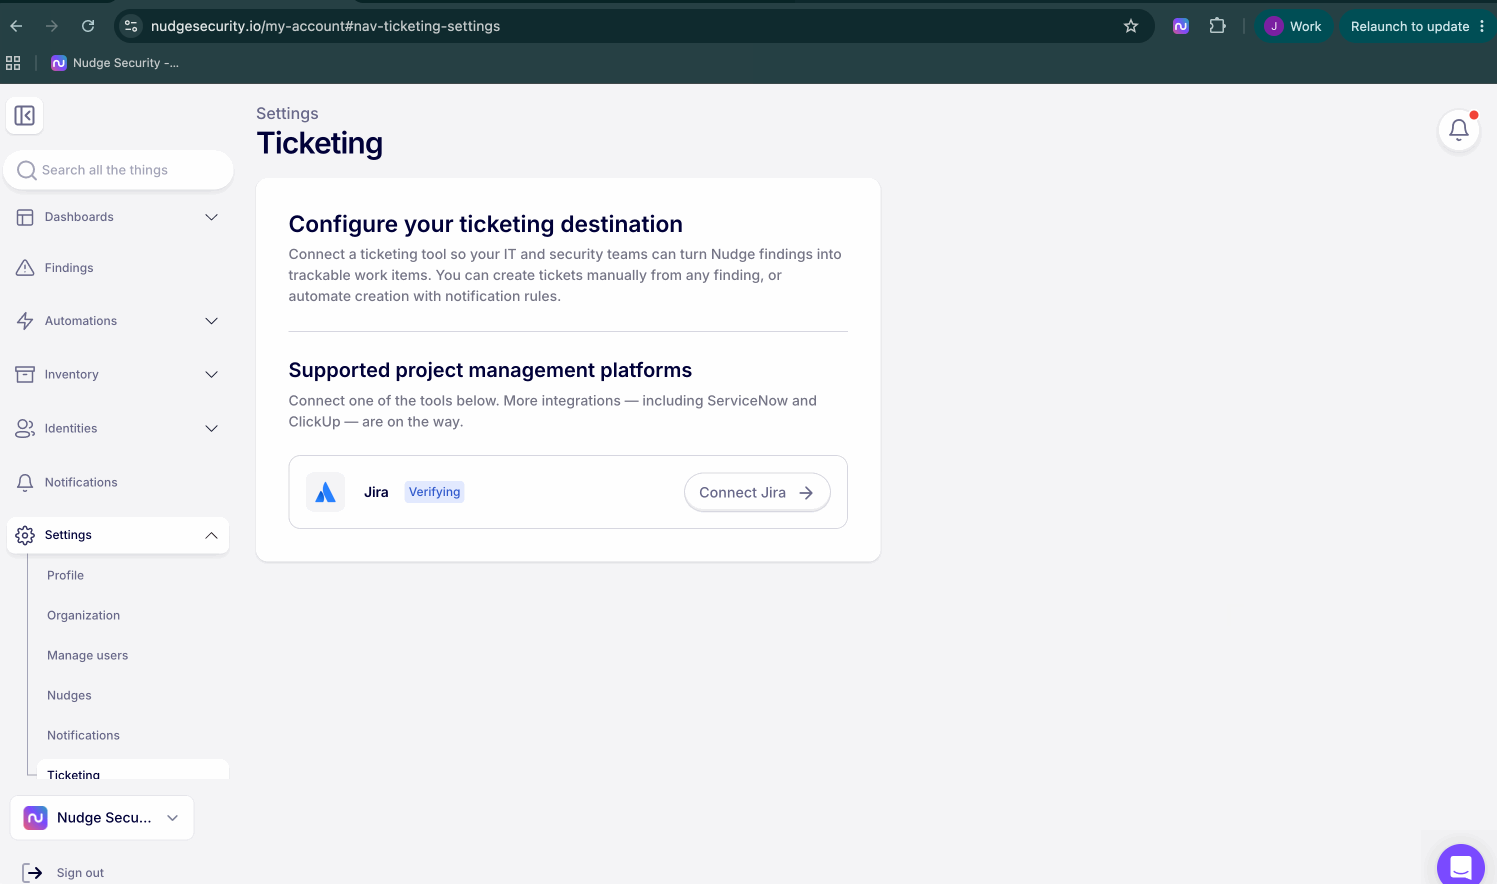
This article covers connecting Jira, mapping your fields, and creating your first ticket. Before you start You'll need admin access in Nudge Security to set up the connection. You'll need a Jira Cloud site. (Jira Data Center / on-prem isn't supported.) One Jira connection is supported per Nudge instance.
 docs update · Oct 2026
· source
- 8 articles Configure the ServiceNow integration Route security findings straight into ServiceNow. Once connected, you can create a ticket from any finding, map it to the right table and fields, and keep both systems in sync—when… docs update · seen Jul 2026 · source
example
-
Connect Jira to Nudge Security so your team can route findings into their existing ticketing workflow.
In the Nudge Security console, go to Settings > Ticketing and connect your Jira instance.Create Jira tickets from your Nudge Security findings · seen Jul 2026 · source
Other 18 capabilities
SaaS and AI risk dashboard shipped Displays a heatmap pairing business criticality tiers with app risk scores and tracks residual risk trends, giving a portfolio-wide view of where risk and business impact overlap across the entire SaaS and AI estate.
release 35 total
-
Adds a
Dashboards > Riskview to quickly identify where exposure is concentrated across your SaaS and AI estate and track changes over time.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Respond dynamically to evolving SaaS and AI risks with adaptive risk management · Sep 2026 · source · release history - Adds a risk dashboard heatmap pairing business criticality tiers with app risk scores to visualize risk concentration across the entire SaaS and AI estate. announced · Sep 2026 · source · release history
- Adds a risk dashboard showing residual risk trends and a heatmap of business criticality versus risk severity across an organization's SaaS and AI portfolio. announced · seen Sep 2026 · source · release history
-
New
Dashboards > Riskdashboard (open beta) shows residual risk scores, a trend chart filterable to business-critical apps, a business-criticality-vs-residual-risk matrix with drill-down, and a ranked highest-risk-apps table built automatically from Nudge's per-app risk scoring. changelog · Aug 2026 · source · release history - Risk trend chart within the dashboard lets you filter historical risk over time to business-critical apps only. See your risk posture at a glance with our new risk dashboard, now in open beta · seen Aug 2026 · source · release history
- Highest-risk apps ranking table surfaces the apps that need attention first, ordered by risk score. See your risk posture at a glance with our new risk dashboard, now in open beta · seen Aug 2026 · source · release history
example
-
Spot where risk and business impact overlap most across your SaaS and AI estate to prioritize deeper vendor reviews.
In the Nudge Security console, open the risk dashboard and use the heatmap to identify apps where a `critical` or `high` business criticality tier intersects with elevated app risk scores.announced · Sep 2026 · source -
Review your SaaS risk posture and identify apps missing approval or carrying high residual risk.
In the Nudge Security console, go to Dashboards > Risk to view tiles for apps assessed, business-critical apps, overall residual risk, and apps missing approval.See your risk posture at a glance with our new risk dashboard, now in open beta · seen Aug 2026 · source
Custom notification triggers shipped Supports sending nudge responses to Slack, email, and webhooks, and configures notifications based on app approval status.
Also counts toward: Outbound webhooks (the product notifies you)
release 9 total
- Enables routing these sensitive data alerts to Slack, Microsoft Teams, email, or a webhook. Get alerted when sensitive data is shared in AI conversations with new notification · Jan 2026 · source · release history
- Allows configuring separate destinations for employee nudges and admin notifications. Configure separate destinations for nudges and notifications · Jan 2026 · source · release history
- Allows configuring alerts based on the type of data detected or at the app level. Get alerted when sensitive data is shared in AI conversations with new notification · Jan 2026 · source · release history
-
Adds
browser nudgecapability to deliver your AI Acceptable Use Policy (AUP) directly in the browser during employee signup or login events. New browser nudge delivers your AI acceptable use policy to help drive safe, compliant AI use in real-time. · Oct 2025 · source · release history -
Enables inviting the Nudge Security app to any Slack channel using the
@Nudge Securitymention Add Nudge Security to your Slack channels using Slack commands · Sep 2025 · source · release history - Adds the ability to deliver policies over Slack or Microsoft Teams Strengthen your AI governance and enforcement with Nudge Security’s AI Acceptable Use Policy playbook. · Sep 2025 · source · release history
docs
- August 20, 2026 Alert your team and nudge end users when a new app is discovered seen Sep 2026 · source
example
-
Add Nudge Security to a specific channel without navigating settings.
@Nudge SecurityAdd Nudge Security to your Slack channels using Slack commands · Sep 2025 · source
Passkey usage and adoption tracking shipped Monitors organization-wide passkey adoption rates, tracks per-employee usage and storage details, and evaluates device-loss survivability and login-verification status to inform authentication strategy and incident readiness.
release
- Passkey usage is also surfaced per individual employee on their user details page. changelog · Aug 2026 · source · release history
- Adds per-employee passkey usage detail on each user's user details page. Track passkey adoption and storage in the new Passkey usage dashboard · seen Aug 2026 · source · release history
-
Adds the
Dashboards > Passkey usagedashboard, showing org-wide passkey adoption rate, top apps used with passkeys, and per-provider storage breakdown with a toggle between number of passkeys and number of users. Track passkey adoption and storage in the new Passkey usage dashboard · seen Aug 2026 · source · release history - Surfaces device-loss survivability and login-verification status for each passkey detected by the browser extension. Track passkey adoption and storage in the new Passkey usage dashboard · seen Aug 2026 · source · release history
- Shows individual employee passkey usage on their user details page Track passkey adoption and storage in the new Passkey usage dashboard · Aug 2026 · source · release history
example
-
Audit where your org's passkeys are stored and whether they survive device loss — useful before a hardware refresh or incident review.
In the Nudge Security console, go to Dashboards > Passkey usage. Use the provider breakdown toggle to switch between 'number of passkeys' and 'number of users', then review the device-loss…Track passkey adoption and storage in the new Passkey usage dashboard · seen Aug 2026 · source -
Navigate to the new dashboard to view organization-wide passkey adoption metrics.
In the console, go to Dashboards > Passkey usageTrack passkey adoption and storage in the new Passkey usage dashboard · Aug 2026 · source
Employee nudge campaigns shipped Runs structured, week-by-week outreach campaigns that send targeted messages to employees via email, Slack, or Microsoft Teams to drive specific behaviors such as SSO enrollment, app review, or policy acknowledgment, and tracks responses in the dashboard.
release
- Bulk nudge sends now report which recipients were skipped due to deleted, archived, or suspended status. changelog · Oct 2026 · source · release history
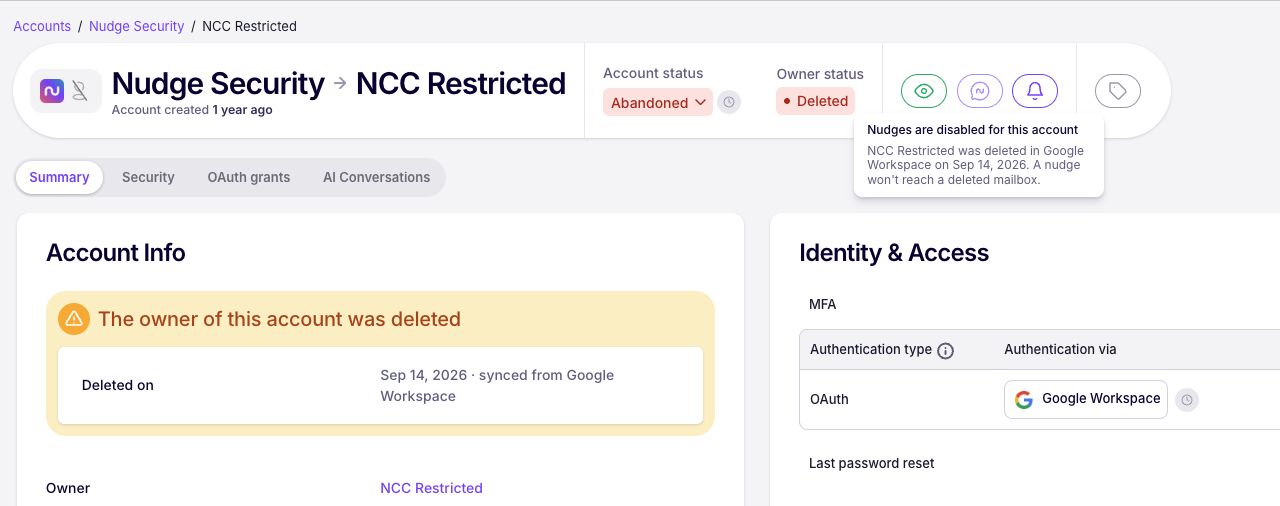
- Nudge Security now blocks sending nudges to deleted, archived, or suspended users and accounts, with the nudge button disabled and a message explaining why delivery is not possible. changelog · Oct 2026 · source · release history
-
Disables the nudge button with an explanatory message when the target user or account is deleted, archived, or suspended.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
 Stop nudging deleted, archived, and suspended users and accounts · Oct 2026
· source
· release history
- Reports skipped recipients when sending bulk nudges to a mix of active and inactive users or accounts. Stop nudging deleted, archived, and suspended users and accounts · Oct 2026 · source · release history
docs
- Choose your nudge campaign Nudge campaigns turn visibility into action. Each campaign is a prescriptive playbook: the nudge templates to use, a week-by-week sequence, success targets, and the talking points to report results up. seen Oct 2026 · source
- Alert your team and nudge end users when a new app is discovered Use this rule to get ahead of shadow IT, understand why new tools are being introduced, and decide whether they need to go through a procurement or review process. seen Oct 2026 · source
AI user remediation and engagement shipped Enables contacting responsible AI tool creators to confirm purpose, justify use, and remediate associated risks directly from risk dashboards.
release
- Governance actions — setting approval status, assigning a technical contact, and nudging the agent creator to confirm intent or remediate — are available directly from the AI agents inventory. announced · Nov 2026 · source · release history
- Send a nudge to an agent's creator to collect a plain-language explanation of the agent's purpose and required access, with the answer saved to the agent's record. Discover and govern AI agents across 23 agentic platforms · Nov 2026 · source · release history
- Adds capability to assign a technical contact to hold accountability for each agent Discover and assess the risk of AI agents with Nudge Security · Mar 2026 · source · release history
- Enables engaging creators directly by nudging the responsible contact to confirm purpose, justify use, and remediate risks Discover and assess the risk of AI agents with Nudge Security · Mar 2026 · source · release history
App inventory filtering shipped Filters the application inventory by up to 27 distinct automatically detected data types and displays filtered risk scores for targeted app analysis.
release
- Enables filtering the app inventory by SSO coverage once custom SSO domains are configured. Set custom SSO domains to track SSO coverage across your apps · Oct 2026 · source · release history
- Adds the ability to filter app inventory by 27 distinct data types without manual research Prioritize your SaaS and AI inventory automatically with data types and business criticality tiers, now in open beta · Jul 2026 · source · release history
- Adds ability to filter the connected app directory by category and capability Connected app experience updates · Apr 2026 · source · release history
- Organizes connected apps alphabetically for easier scanning Connected app experience updates · Apr 2026 · source · release history
Custom SSO domain configuration and auto-approval shipped Configures custom SSO domains and identity integrations to automatically identify authenticated applications, populate SSO provider fields in the inventory, and enable auto-approval workflows for newly onboarded apps.
release
- Enables auto-approval of apps that users sign into through a configured custom SSO domain. Set custom SSO domains to track SSO coverage across your apps · Oct 2026 · source · release history
-
Adds custom SSO domain configuration via
Settings > Browser extension, letting the browser extension recognise logins through those domains and automatically fill in the SSO provider for each app — even without a connected identity provider.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Set custom SSO domains to track SSO coverage across your apps · Oct 2026 · source · release history
docs
- Updated over a week ago Note: If you've connected the Onboard apps to Okta playbook or you're using Entra ID we will auto-approve any apps that are onboarded onto Okta or Entra ID. seen Aug 2026 · source
example
-
Add a custom SSO domain so the browser extension automatically identifies SSO-authenticated apps and populates the SSO provider field in your inventory — no identity-provider integration required.
In the Nudge Security console, go to Settings > Browser extension and add your custom SSO domain (e.g. sso.example.com) to the custom SSO domains list.Set custom SSO domains to track SSO coverage across your apps · Oct 2026 · source
Risk-to-action remediation panel shipped Ranks specific control gaps by their potential risk reduction and surfaces direct remediation actions within the panel so operators can address the highest-impact gaps first.
release
- Adds a risk-to-action panel that ranks specific control gaps (such as enabling SSO or closing stale OAuth grants) by their potential risk reduction, with direct remediation actions available from within the panel. announced · seen Sep 2026 · source · release history
- Adds adaptive controls that adjust security decisions automatically through native controls, policy-driven nudges, agent-powered workflows, guided remediation, and third-party security integrations. Respond dynamically to evolving SaaS and AI risks with adaptive risk management · Sep 2026 · source · release history
- Ranks recommended actions by projected residual risk reduction to guide remediation priorities. Know your real vendor risk with inherent and residual risk scores, now in open beta · Jul 2026 · source · release history
- Shows specific controls violated within the finding detail panel Security posture findings now mapped to compliance frameworks · Jun 2026 · source · release history
AI agent configuration risk analysis shipped Surfaces high-risk agentic configurations such as hardcoded credentials, unauthenticated connections, and publicly accessible agents in AI usage overviews.
Shared capability: Secret scanning
release
- Flag risky AI agents that are publicly accessible, carry hardcoded credentials, use unauthenticated MCP connections, or whose creators have left the organization. Discover and govern AI agents across 23 agentic platforms · Nov 2026 · source · release history
- Surfaces agentic risks such as publicly accessible agents, hardcoded credentials, unauthenticated MCP connections, and connections to high-risk apps Discover and assess the risk of AI agents with Nudge Security · Mar 2026 · source · release history
example
-
Review all discovered AI agents in one place to spot agents with hardcoded credentials or unauthenticated MCP connections before they become an incident.
In the Nudge Security console, go to Identities > AI agents, then filter by risk flags such as 'hardcoded credentials' or 'unauthenticated MCP connections' to triage agents that need immediate…Discover and govern AI agents across 23 agentic platforms · Nov 2026 · source
Enhanced external file share management shipped Expands visibility into Google Drive external shares by identifying orphaned or inactive files and allows prioritized filtering and scope-confirmed revocation of access.
release
- Adds Inventory > External File Shares view to spot orphaned Shared Drives, shares to personal email, files owned by deactivated employees, and shares with no activity in 90 days Discover and revoke risky external file shares in Google Drive · Jul 2026 · source · release history
- Adds filtering capability to prioritize cleanup by domain or specific external company for external file shares Discover and revoke risky external file shares in Google Drive · Jul 2026 · source · release history
- Adds per-item actions to tighten or revoke access with scope confirmation for external file shares Discover and revoke risky external file shares in Google Drive · Jul 2026 · source · release history
Agentic AI data flow visibility shipped Maps SaaS-to-AI data movements via an interactive chart, highlights high-volume transfers, and allows ranking data flows by volume to identify excessive data consumption.
release
- Allows ranking AI data flows by data volume, file count, or user count to identify which AI tools consume the most corporate data. See how data flows from source SaaS apps to AI conversation tools · Feb 2026 · source · release history
- Adds an interactive chart in the AI Usage Dashboard that maps file uploads and copy/paste actions from SaaS applications to AI conversation tools. See how data flows from source SaaS apps to AI conversation tools · Feb 2026 · source · release history
- Enables spotting high-volume data movements and potential risks in the new AI Usage Dashboard card. See how data flows from source SaaS apps to AI conversation tools · Feb 2026 · source · release history
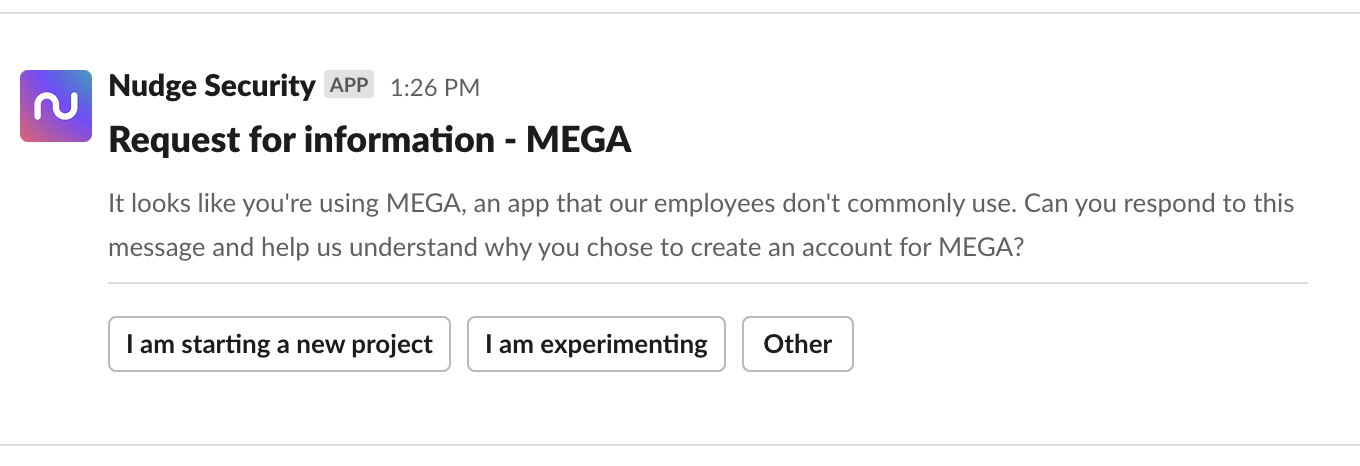
Slack integration documented Connects to Slack so operators can send nudges directly to employees in Slack, employees can respond without leaving the app, and the dashboard receives response tracking and custom notification alerts such as new breach events.
docs
-
Nudge integrates with Slack in an effort to help you reach employees right where they’re working. With this functionality, you can: Send nudges to users in Slack, so users can respond directly from the app for Slack Track users’ responses within your Nudge Security dashboard Receive Slack messages based on your custom…
 docs update · Oct 2026
· source
- Nudge integrates with Slack in an effort to help you reach employees right where they’re working. With this functionality, you can: Send nudges to users in Slack, so users can respond directly from the app for Slack Track users’ responses within your Nudge Security dashboard Receive Slack messages based on your… seen Oct 2026 · source
Supply chain breach visibility shipped Identifies impacted vendors and surfaces vendor names in security views during detected supply chain breaches.
release
- Adds the impacted vendor name to the supply chain card view during a detected supply chain breach Know which vendors were breached in an app’s supply chain · Jun 2025 · source · release history
- Adds tooltip showing the impacted vendor name in the security tab when a supply chain breach is detected Know which vendors were breached in an app’s supply chain · Jun 2025 · source · release history
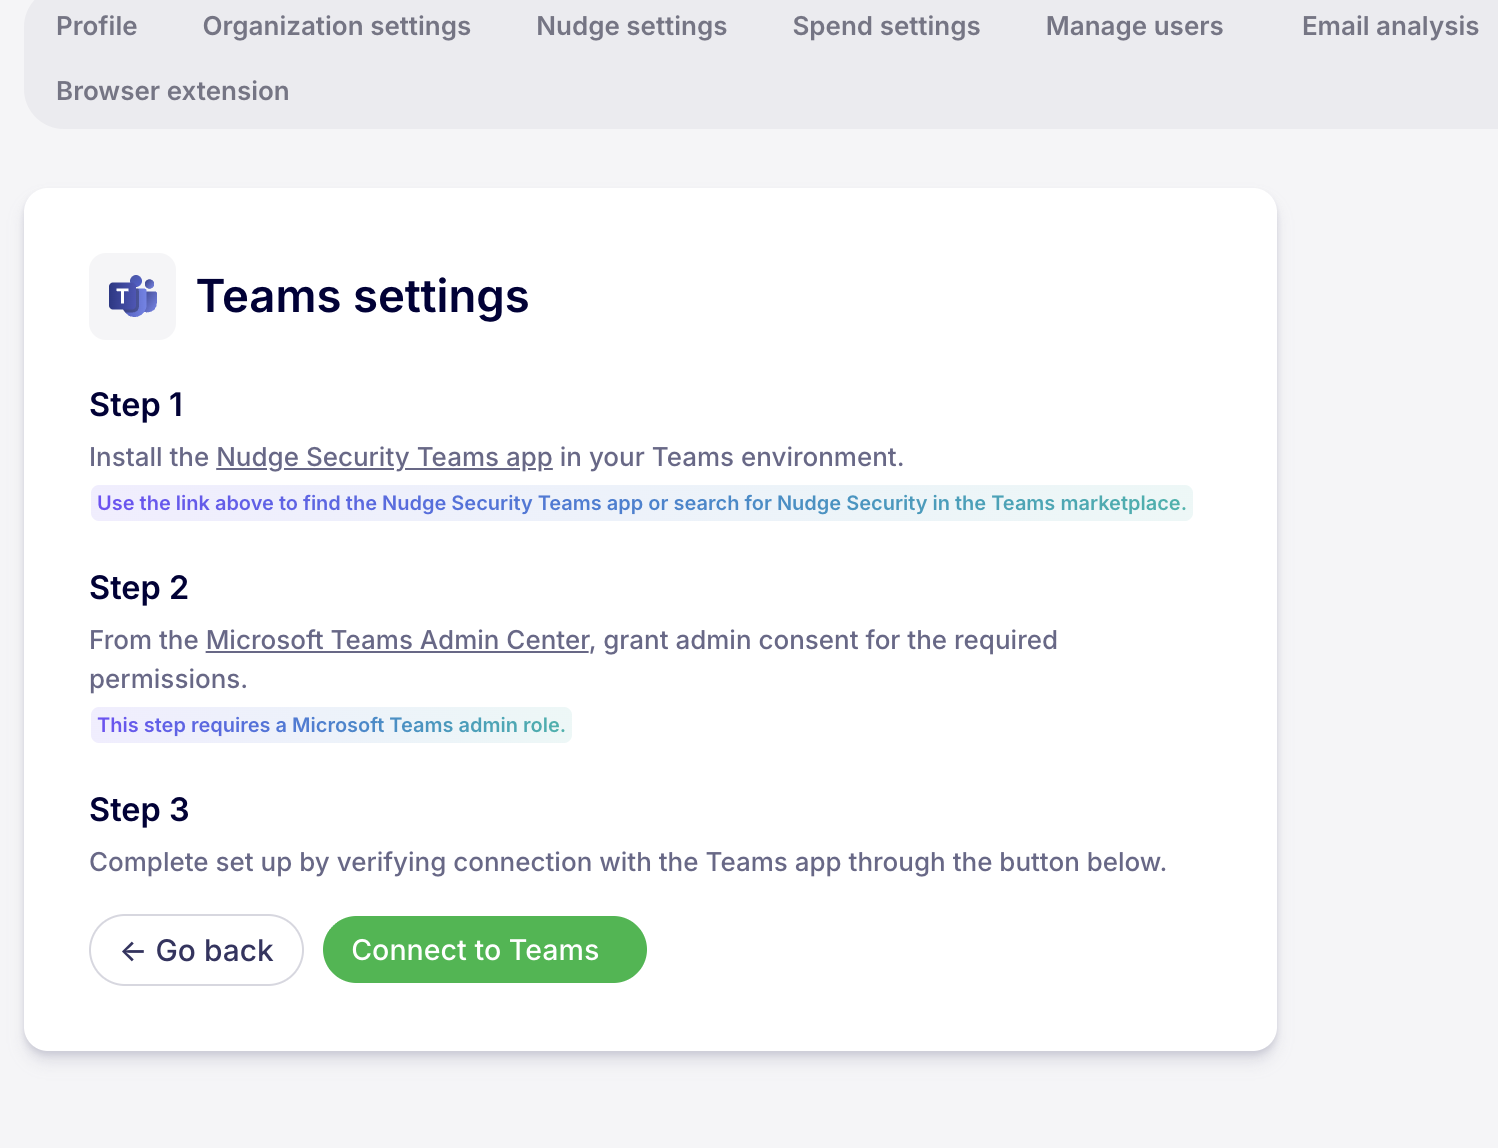
Microsoft Teams integration documented Connects to Microsoft Teams so operators can send nudges to employees in Teams, employees can respond directly from the Teams app, and the dashboard receives custom notification alerts such as new breach events.
docs
-
Nudge integrates with Microsoft Teams to help you reach employees right where they're working. With this functionality, you can: Send nudges to users in Teams, so users can respond directly from the Teams app instead of email Receive Teams messages based on your custom notification rules, such as when a new breach…
 docs update · Oct 2026
· source
Extended MCP grant risk analysis shipped Explores and visualizes scopes and permissions of remote Model Context Protocol connections to assess risk in AI agent integrations.
release
- Expanded OAuth risk insights to discover and visualize scopes/permissions of remote Model Context Protocol (MCP) connections powering AI agents Gain visibility into risky MCP connections with new OAuth risk insight · Feb 2026 · source · release history
SaaS spend management shipped Tracks subscriptions, identifies apps with many individual licenses, and provides financial forecasts to manage costs.
release
- Adds a new card to the spend dashboard identifying SaaS apps with many individual subscriptions. Identify apps with a high number of individual subscriptions in the spend dashboard · May 2025 · source · release history
Browser extension deployment and management documented Supports configuration and deployment of the browser extension to managed devices via MDM for consistent rollouts and policy enforcement.
docs
- This guide covers deploying the Nudge Security browser extension for Safari to Macs you manage with an MDM. seen Sep 2026 · source
Employee-facing app discovery context documented Presents employees with a lightweight explanation of how the tool monitors software usage across the organization, helping them understand what data is collected and why, to reduce friction when they receive nudges or access reviews.
docs
- Your organization uses Nudge Security to keep track of the software and web apps people across the company are using. It helps your IT and security teams understand what's out there, spot potential risks, and guide employees toward safer choices — without getting in your way. seen Oct 2026 · source
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for Nudge Security, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Nudge Security puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Commercials
pricing & packaging history · Nudge Security vendor page23 readings of Nudge Security's pricing page since Dec 2022, with 13 relaunches of its plan lineup and 6 changes to what its plans include — each one dated, compared with the reading before it, and explained for someone buying the tool.
Pricing and packaging history is included with Researcher and Business. See how every vendor we track sells, and how that has changed over time, using data we don't publish anywhere else.
See plans → Already subscribed? Sign in →Plans by offering
Each offering on the pricing page links to its own page of plans, read at its latest capture.
Plan relaunches
Plans, prices and descriptions are quoted from the vendor's own pricing page as we read it on each date. A plan missing from a later reading is shown as no longer listed on the page — a statement about the page, not the product. Readings that failed to show any plans are left out rather than read as a change.
Website history
nudgesecurity.com, every changeNudge Security's home and pricing pages and 41 more pages as they looked each month from December 2021 to October 2026: 63 renders, 14 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Coverage
Missing something? Tell us
What Nudge Security connects to, runs on and detects, read from its release notes and docs. So far: 9 new integrations, 3 new detections.
12 changes, tracked since Sep 30, 2026.
-
Nov 32026
new Cryptocurrency wallet address detection in AI conversations
With cryptocurrency wallet addresses, cryptocurrency identifiers
AI conversation monitoring now detects cryptocurrency wallet addresses and related cryptocurrency identifiers, in addition to the PII, secrets, and financial info it already catches.
-
Nov 32026
new Duo Security connected app
We've added a new connected app for Duo Security . Connect this app to Nudge Security to centralize visibility into accounts, activity, and misconfigurations across your critical SaaS stack.
-
Nov 22026
new AI agent discovery via API connections
Adds Abacus.AI, ChatGPT, Claude managed agents, Gemini, LangSmith Fleet, Microsoft Copilot Studio, n8n, Notion AI agents and 4 more. 12 in all.
API-based discovery: Abacus.AI, ChatGPT, Claude managed agents, Gemini, LangSmith Fleet, Microsoft Copilot Studio, n8n, Notion AI agents, Salesforce Agentforce, ServiceNow, Tines, and Workato.
-
Nov 22026
new AI agent discovery via browser extension
Adds Amazon Quick, Atlassian Rovo, ChatGPT workspace agents, Cursor automations, Datadog, HubSpot, HyperAgent, OpenAI Agents Workflows and 3 more. 11 in all.
Browser-based discovery: Amazon Quick, Atlassian Rovo, ChatGPT workspace agents, Cursor automations, Datadog, HubSpot, HyperAgent, OpenAI Agents Workflows, Retool, Zapier Agents, and Zoom AI Workflows.
-
Oct 292026
new Notion AI agent discovery
Nudge Security now discovers AI agents your team builds on Notion. This is available as part of the AI agent discovery research preview. To get started, enable the Notion AI agents connected app in Nudge Security.
-
Oct 212026
new Microsoft Entra ID SSO via OIDC
With OpenID Connect
This guide walks you through creating an app registration in Microsoft Entra ID (formerly Azure Active Directory) so your team can sign in to Nudge Security with their Microsoft credentials using OpenID Connect (OIDC).
-
Oct 212026
new Microsoft Teams integration
Nudge integrates with Microsoft Teams to help you reach employees right where they're working. With this functionality, you can: Send nudges to users in Teams, so users can respond directly from the Teams app instead of email Receive Teams messages based on your custom notification rules, such as when a new breach affects your organization's supply chain or a user signs up for a new application
-
Oct 212026
new Slack integration
Nudge integrates with Slack in an effort to help you reach employees right where they're working.
-
Oct 212026
new Okta SSO integration
Supported Features Service Provider (SP)-Initiated Authentication (SSO) Flow - This authentication flow occurs when the user attempts to log in to the application from Nudge Security. Identity Provider (IDP)-Initiated Authentication (SSO) Flow - This authentication flow occurs when the user attempts to log in to Nudge Security from Okta.
-
Oct 212026
new Okta connected app integration
The Okta connected app uses an API integration between Nudge Security and Okta in order to share information and perform certain actions between the two services.
-
Sep 302026
new Browser Extension Risk Detection
With browser extensions
It's built to inspect the artifacts and metadata behind installed browser extensions and flag the ones that are malicious, compromised, risky or otherwise don't do what they claim
-
Sep 302026
new OAuth Grant Risk Detection
With OAuth grants
Designed to review new integration OAuth grants as Nudge Security discovers them and resolve overly permissive and high-risk ones
Chat & assistant apps 1
Model providers & gateways 1
Identity & access 2
Observability & monitoring 1
Chat & collaboration 2
Ticketing & ITSM 1
Other 22
Nothing first seen in this window. That doesn't mean Nudge Security shipped nothing, only that we found no record of it.
How we count
Read from 18 of 225 release notes and docs updates we hold for Nudge Security. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through Nudge Security's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
225 entries
No entries match these filters.
- November 20264
- October 202618
- September 202613
- August 20269
- July 202628
- June 20265
- May 20265
- April 20267
- March 20263
- February 20266
- January 20267
- December 20253
- November 20254
- October 20257
- September 20258
- August 20251
- July 20254
- June 20256
- May 20254
- April 20256
- March 20255
- February 20256
- January 20253
- December 20242
- November 20242
- October 20244
- September 20242
- August 20243
- July 20242
- June 20241
- May 20243
- April 20242
- March 20242
- February 20242
- December 20232
- November 20233
- October 20236
- September 20235
- August 20235
- July 20233
- June 20231
- May 20232
- April 20233
- March 20235
- February 20233
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →