Ping Identity
changelog-20261029-07d5f16d commercialThe section your link pointed to isn't on Ping Identity's page any more, so we've brought you to the top.
Ping Identity is an identity and access management platform providing authentication, single sign-onsingle sign-onSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management., multi-factor authenticationmulti-factor authenticationMulti-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone., and identity governance services.
callbacksBuilder.qrCodeCallback()
Replace your existing widget script tag:
<script src="https://assets.pingone.<region>/davinci/latest/v2/davinci.js"></script>
or, to exclude DaVinci CSS rules:
<script src="https://assets.pingone.<region>/davinci/latest/v2/davinci-no-css.js"></script>
{
  "userAgent": "MyCompanyIntegration/1.0"
}
esv.am.secrets.gsm.stableid.version.only=true
esv.am.secrets.gsm.stableid.version.only=true
<Journey JSON snippet>
'nodeId': 'mfa-qr',
'nodeType': 'CombinedMFANode',
'useJavaScript': false
</Journey JSON snippet>
<External REST Service Config>
'userAgent': 'MyApp-Connector/1.0'
</External REST Service Config>
curl -X POST \
  'https://<tenant>.forgeblocks.com/am/json/realms/root/realm-config/secrets/stores/<store-id>/mappings/<mapping-id>?_action=validate' \
  -H 'Authorization: Bearer <access-token>' \
  -H 'Content-Type: application/json'
curl -X PUT 'https://<tenant-env-fqdn>/am/json/realms/root/realms/alpha/realm-config/authentication/authenticationtrees/nodes/UsernameCollectorNode/2.0' -H 'Accept-API-Version: protocol=2.1,resource=3.0' -d '{...}'
curl -H 'Accept-API-Version: protocol=2.1,resource=3.0' https://<tenant-env-fqdn>/am/json/realms/root/realm-config/authentication/authenticationtrees/nodes/UsernameCollectorNode/2.0
curl -X POST 'https://<pingone-env-id>/environment/aiagent?_action=enable' -H 'Authorization: Bearer <access_token>'
curl -X POST 'https://<aic-host>/idp/rest/realm-config/services/pingOneWorkerService/workers/<pingone-worker-service-name>?action=testConnection' -H 'Authorization: Bearer <token>'
curl -X GET 'https://<aic-host>/idp/rest/realm-config/authentication/authenticationtrees/nodes?action=listLatestNodeDefinitions' -H 'Authorization: Bearer <token>'
curl -X PUT 'https://<aic-host>/idp/rest/realm-config/services/pingIdentityPingOneProtectEvaluation' -H 'Content-Type: application/json' -d '{"customDeviceId": "<device-id>", "customBrowserCookie": "<cookie-name>"}'
Summary
Ping Identity is a commercial identity-access platform, delivered as a hosted cloud service (PingOne) alongside self-hosted server products (PingFederate, PingAM, PingIDM, PingDirectory), that handles authentication, single sign-on, directory services, and adaptive MFAMFAMulti-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone.. It is aimed at identity and access management teams and the developers who integrate applications against its APIs and SDKs, rather than at end users directly. Its own documentation organizes the product line by function — federation and SSOSSOSingle sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management., directory data at scale, orchestration journeys, and now agent identity for AI systems — spanning cloud and on-premises deployments under one vendor rather than pointing to a single named competitor. Recent changes include Rich Authorization Request support in OAuth 2.0OAuth 2.0An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms., secret-store integration for scripted journeys, and admin-console controls for social identity providersidentity providersA service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. and Proxy Connect, suggesting active, incremental development.
Ping Identity is an identity and access management platform providing authentication, single sign-on, multi-factor authentication, and identity governance services.
How Ping Identity helps
Which of my AI agents are acting with credentials nobody scoped for them?
assigns agent identities under the Identity for AI framework and enforces least-privilege, delegated access at runtime, flagging agent behavior that falls outside the granted scope
Which OAuth clients can request more authorization than they should?
lets you configure Authorization Detail Type settings per client so a client's Rich Authorization Request is checked against the detail types it is explicitly allowed to declare, rejecting the rest
Can my scripted journeys reach a stored secret without putting it in the script?
resolves a managed secret reference at runtime through a secret-store binding, and a validation action confirms the mapping resolves before the journey depends on it in production
Are my Microsoft 365 SSO logins using the right username attribute after a config change?
applies the selected UPN Attribute Name setting during WS-Trust authentication, but only for applications that have been resaved since the change, so unresaved apps keep the old behavior
Which social identity providers and Proxy Connect settings can I change without calling the API?
exposes creation, editing, and configuration of social identity providers and Proxy Connect directly in the admin console, so routine changes no longer require a scripted API call
Languages
Features
Built from Ping Identity's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
What Ping Identity offers you
- Web management console10
- REST API3
- Administrative audit log2
- JavaScript scripting support2
- Multi-factor authentication2
- Scripting API2
- Scripting language support2
- MCP server1
- ML-based detection1
- Natural-language query1
- Role-based access control1
- Single sign-on1
No capabilities match.
OIDC SSO 2 features Identity and access since 2026
HTTP POST support for OIDC RP-initiated sign-offs documented Applications can initiate OIDC sign-out using an HTTP POST request, not only an HTTP GET.
Shared capability: OIDC SSO
docs
-
August 2026 August 5 HTTP POST support for app-initiated sign-offs
/as/signoff endpoint now accepts HTTP POST requests in addition to HTTP GET requests for OpenID Connect (OIDC) relying party (RP)-initiatedsign-offs. This endpoint provides more options when configuring how your applications handle user sign-offs. docs update · Aug 2026
· source
-
August 2026 August 5 HTTP POST support for app-initiated sign-offs
/as/signoff endpoint now accepts HTTP POST requests in addition to HTTP GET requests for OpenID Connect (OIDC) relying party (RP)-initiatedsign-offs. This endpoint provides more options when configuring how your applications handle user sign-offs. docs update · Aug 2026 · source
Evaluator Version selector for next-generation script types shipped The Evaluator Version selector for choosing the script runtime is available for a broader set of script types in the admin console.
Shared capability: OIDC SSO
Also counts toward: Web management console
release
- Extends the Evaluator Version selector in the admin console to all remaining next-generation script types: OIDC node, Social Provider Handler node, OAuth2 scripts, and Policy Condition scripts. 08 Jul 2026 (2026-07-09) · Jul 2026 · source · release history
- Evaluator Version selector available for OIDC node, Social Provider Handler node, OAuth2 scripts, and Policy Condition scripts 08 Jul 2026 · Jul 2026 · source · release history
Single sign-on 1 feature Identity and access since 2026
Microsoft 365 SSO UPN attribute for WS-Trust authentication shipped Microsoft 365 SSO applications correctly use the administrator-selected UPN attribute when authenticating users via WS-Trust.
Shared capability: Single sign-on
Also counts toward: Single sign-on
release
- Microsoft 365 SSO applications now use the selected UPN Attribute Name setting for WS-Trust username authentication; existing applications must be resaved for this change to take effect. 08 Jul 2026 (2026-07-09) · Jul 2026 · source · release history
- Microsoft 365 SSO applications now use the selected UPN Attribute Name setting for WS-Trust username authentication (existing applications must be resaved). 08 Jul 2026 (2026-07-09) · Jul 2026 · source · release history
SAML SSO 1 feature Identity and access since 2026
SAML metadata import with optional signature verification skip shipped SAML metadata can be imported with the option to bypass signature verification when needed.
Shared capability: SAML SSO
release 9 total
- Adds support for skipping XML signature verification when importing remote SAML 2.0 provider metadata.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ changelog · Oct 2026 · source · release history
- Adds option to skip XML signature verification when importing remote SAML 2.0 provider metadata. changelog · Oct 2026 · source · release history
- Adds ability to skip XML signature verification when importing remote SAML 2.0 provider metadata. 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history
- Adds the ability to skip XML signature verification when importing remote SAML 2.0 provider metadata via a new option in the import workflow (OPENAM-26718) 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history
- Adds the ability to skip signature verification when importing SAML metadata (OPENAM-26721). changelog · Aug 2026 · source · release history
- SAML metadata import now supports skipping signature verification. changelog · Jul 2026 · source · release history
example
-
Skip XML signature verification when importing a remote SAML 2.0 metadata document from a provider that does not sign its metadata.
In the Advanced Identity Cloud admin console, go to Federation > Remote Entity Providers, import a SAML 2.0 provider metadata URL, and enable the option to skip XML signature verification before…changelog · Oct 2026 · source -
Skip signature validation when federating with a partner whose SAML 2.0 metadata lacks a valid XML signature, avoiding import failures.
In the admin console, go to Federation > Entity Providers > Import Remote Provider, upload the metadata file, and enable 'Skip XML signature verification' before saving.28 Sep 2026 (2026-09-29) · Sep 2026 · source -
Skip signature checks for a remote SAML identity provider metadata import.
// In the admin console, when importing remote SAML 2.0 metadata, use the 'skip XML signature verification' option28 Sep 2026 · Sep 2026 · source
Other / not yet classified 99 features Features we have not matched to a capability yet. A suggested match is marked.
Rich Authorization Requests (RFC 9396) support shipped OAuth 2.0 clients can use Rich Authorization Requests to declare and restrict the specific authorisation details they require.
release 16 total
-
The OpenID Connect discovery endpoint now always returns
authorization_response_iss_parameter_supported: true, and authorization responses (including error responses) now include theissparameter so clients can verify the response issuer. changelog · Oct 2026 · source · release history -
Enables omission of the
scopeparameter in authorization code requests (including PAR) whenauthorization_detailsare requested and Rich Authorization Requests with RCS is enabled. 22 Oct 2026 (2026-10-23) · Oct 2026 · source · release history -
Allows access tokens to include
authorization_detailsfor authorization code and refresh token grants 14 Sep 2026 (2026-09-15) · Sep 2026 · source · release history -
Dynamic client registration requests now support
authorization_details_typesto declare the authorization detail types a client supports at registration time. changelog · Jul 2026 · source · release history -
New realm-level OAuth2 Provider setting enables Rich Authorization Requests (RFC 9396) processing when an RCS is configured, and controls advertisement of
authorization_details_types_supportedon the well-known endpoint. changelog · Jul 2026 · source · release history -
Individual OAuth 2.0 clients can now be configured with
Authorization Detail Type(s)to restrict which authorization detail types each client may request. changelog · Jul 2026 · source · release history
example
-
Restrict which authorization detail types a specific OAuth 2.0 client may request, scoping RAR to only the types relevant to that client.
In the Admin console, go to Applications > OAuth 2.0 Clients > <your client> > Advanced and set the 'Authorization Detail Type(s)' field to the permitted types, then save.20 Jul 2026 (2026-07-21) · Jul 2026 · source -
Configure an OAuth 2.0 client to request specific authorization detail types.
'Authorization Detail Type(s)'20 Jul 2026 (2026-07-21) · Jul 2026 · source -
Configure a realm to support RFC 9396 Rich Authorization Requests.
'Enable Rich Authorization Requests with RCS'20 Jul 2026 (2026-07-21) · Jul 2026 · source
Declarative Identity Governance Certification shipped Reviewers can certify identity profiles and role compositions via dedicated task views, enabling governance of records rather than just access.
release 10 total
- Adds dedicated IGA certification review task views for identity-profile and role-composition items, letting reviewers examine and decide on each item type separately. changelog · Sep 2026 · source · release history
- Adds IGA role composition certification, enabling reviewers to certify role definitions including attributes, glossary data, entitlements, applications, and membership rules. changelog · Sep 2026 · source · release history
- Adds IGA identity profile certification, enabling reviewers to certify identity records including external users and AI agents — not just access. changelog · Sep 2026 · source · release history
- IGA role composition certification enables reviewers to certify role definitions, including attributes, glossary data, entitlements, applications, and membership rules. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
- IGA identity profile certification enables reviewers to certify identity records — including external users and AI agents — rather than access alone. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
- IGA identity profile certification enables reviewers to certify identity records, including external users and AI agents, rather than access alone. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
example
-
Certify role definitions including entitlements.
1. Navigate to the IGA Certification Review views in the admin console. 2. Select 'Role Composition' tab. 3. Certify attributes, glossary data, and membership rules.02 Sep 2026 (2026-09-03) · Sep 2026 · source -
Review external user identity records for certification.
1. Navigate to the IGA Certification Review views in the admin console. 2. Select 'Identity Profile' tab. 3. Review records for 'external users' and 'AI agents'.02 Sep 2026 (2026-09-03) · Sep 2026 · source
AI agent identities shipped Dedicated identities can be created specifically to represent and secure AI-driven solutions within the platform.
release 8 total
- Adds search and sort capabilities for the list of AI agent identities. changelog · Oct 2026 · source · release history
- Adds search and sort capabilities for the list of AI agent identities. 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history
- Supports OAuth 2.0 Client ID Metadata Documents (CIMD), allowing AI agents and external clients to identify themselves via a hosted metadata document without prior or dynamic client registration. 14 Sep 2026 (2026-09-15) · Sep 2026 · source · release history
- Adds IGA correlation rules for unmanaged applications, letting administrators link aggregated accounts to identities during account aggregation. changelog · Sep 2026 · source · release history
- Introduces AI agent identities to secure AI-driven solutions. changelog · Aug 2026 · source · release history
- Identity Governance for AI agents (IGA-4223): Detects, onboards, and governs AI agents alongside human identities using Agent Governance. 04 Jun 2026 (2026-06-05) · Jun 2026 · source · release history
docs
- 14 Sep 2026 Version 23604.0 Support for OAuth 2.0 Client ID Metadata Documents (CIMD) (AME-33561) Advanced Identity Cloud now supports CIMD. This allows AI agents and other external clients to identify themselves through a hosted metadata document instead of requiring prior registration or dynamic client registration. changelog · Sep 2026 · source
-
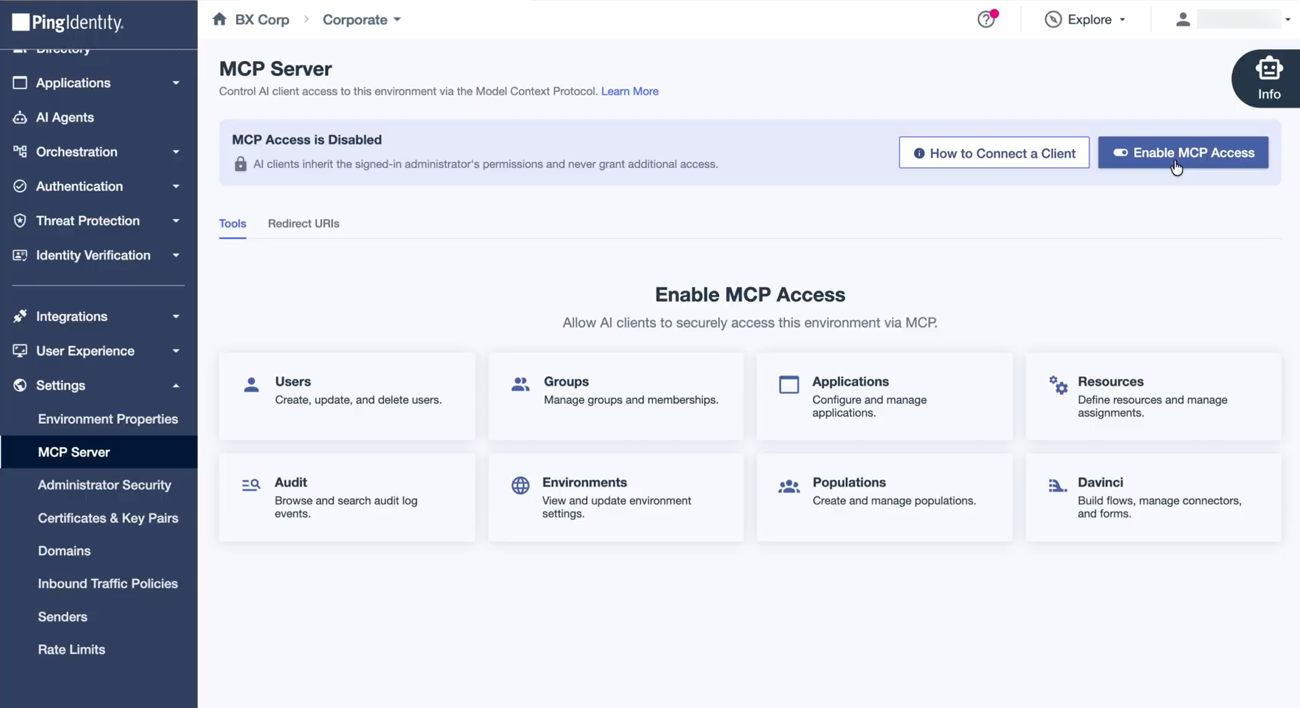
Expand/Collapse All PingOne Remote MCP Server (early access) The PingOne Remote MCP Server is now available for early access (EA). The PingOne Remote MCP Server lets artificial intelligence (AI) clients connect to PingOne through a single remote Model Context Protocol (MCP) endpoint.
 docs update · Sep 2026
· source
example
-
Govern AI agents alongside human identities in Identity Governance.
Use Agent Governance to detect and onboard AI agents04 Jun 2026 (2026-06-05) · Jun 2026 · source
Optional parameters in custom reports shipped Individual parameters in custom reports can be marked as optional, making it easier to run reports without supplying every value.
release 8 total
- In Advanced Reporting, parameters such as status, journeys, and roles are now optional in several out-of-the-box reports, so you can run them without selecting values you don't need.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ 15 Oct 2026 (2026-10-15) · Oct 2026 · source · release history
- Adds the ability to mark parameters in custom reports as optional, giving more flexibility when running reports (IAM-10610). changelog · Aug 2026 · source · release history
- Custom report parameters can now be marked as optional, providing more flexibility when running reports. changelog · Jul 2026 · source · release history
- Supports marking parameters in custom reports as optional, enabling more flexible report execution. 16 Jul 2026 (2026-07-17) · Jul 2026 · source · release history
- Custom reports now support marking parameters as optional 16 Jul 2026 (2026-07-17) · Jul 2026 · source · release history
- You can now mark parameters in custom reports as optional, giving you more flexibility when running reports 16 Jul 2026 · Jul 2026 · source · release history
example
-
Configure custom reports to accept optional parameters for flexible execution.
In the admin console, edit a custom report and toggle the 'Optional' setting on desired parameters.16 Jul 2026 (2026-07-17) · Jul 2026 · source
Microsoft Entra ID and custom SMTP email provider configuration shipped Microsoft Entra ID or custom SMTP email providers can be configured in the admin console, with the ability to send a test email to verify delivery before use.
Also counts toward: Web management console
release
- Adds ability to configure Microsoft Entra ID or custom SMTP email providers and send test emails from the Advanced Identity Cloud admin console. changelog · Oct 2026 · source · release history
- Adds support for configuring Microsoft Entra ID or custom SMTP email providers in the Advanced Identity Cloud admin console, with the ability to send test emails. changelog · Oct 2026 · source · release history
- Enables configuring Microsoft Entra ID or custom SMTP email providers and sending test emails from the Advanced Identity Cloud admin console (IAM-10741) 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history
- Enables configuration of Microsoft Entra ID or custom SMTP email providers and test-email sending from the Advanced Identity Cloud admin console. 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history
example
-
Route outbound identity emails through Microsoft Entra ID or a custom SMTP server and verify delivery with a test email before going live.
In the Advanced Identity Cloud admin console, go to Email Provider settings, select 'Microsoft Entra ID' or 'Custom SMTP', fill in the connection details, then click 'Send Test Email' to confirm.changelog · Oct 2026 · source -
Configure Microsoft Entra ID or a custom SMTP provider as your email sender and verify delivery with a test email — useful when onboarding a new tenant or switching email infrastructure.
In the Advanced Identity Cloud admin console, go to Email Provider settings, select 'Microsoft Entra ID' or 'Custom SMTP', fill in the connection details, then click 'Send Test Email' to verify.changelog · Oct 2026 · source -
Configure a custom SMTP email provider and validate it works before relying on it for production identity journeys.
In the Advanced Identity Cloud admin console, go to Email Provider settings, select 'Custom SMTP' or 'Microsoft Entra ID', enter your provider credentials, then click 'Send Test Email' to verify…changelog · Oct 2026 · source -
Configure a Microsoft Entra ID or custom SMTP email provider and verify delivery with a test email before rolling out to users.
In the Advanced Identity Cloud admin console, go to Settings > Email Provider, select 'Microsoft Entra ID' or 'Custom SMTP', fill in the connection details, then click 'Send Test Email' to confirm.28 Sep 2026 (2026-09-29) · Sep 2026 · source
Attribute mapping for custom resource scopes shipped Administrators can map specific attributes to custom resource scopes, controlling what data appears in access tokens based on what the client requests.
release
- Backchannel transactions now record the authenticated subject on completion even when no session is created, preserving any subject declared before authentication. 14 Sep 2026 (2026-09-15) · Sep 2026 · source · release history
-
Enables issuance of access tokens with
authorization_detailsthrough the authorization code and refresh token grants when details were granted during authorization. 14 Sep 2026 (2026-09-15) · Sep 2026 · source · release history -
Adds Allow audience members to introspect tokens setting on the OAuth 2.0 provider, permitting any client whose
client_idappears in a token'saudclaim to introspect that token without a special scope. 14 Sep 2026 (2026-09-15) · Sep 2026 · source · release history -
oauth2.providerintroduces Allow audience members to introspect tokens setting enabling any client in a token’saudclaim to introspect that token. 14 Sep 2026 · Sep 2026 · source · release history -
oauth2.providerallows access tokens to includeauthorization_detailsfor authorization code and refresh token grants when details were granted during authorization. 14 Sep 2026 · Sep 2026 · source · release history - Backchannel transactions now record the authenticated subject on completion even when no session is created, preserving pre-authentication subjects. 14 Sep 2026 · Sep 2026 · source · release history
docs
-
August 11 Attribute mapping for custom resource scopes You can now map attributes to scopes defined for a custom resource. This capability allows you to control which attributes are included in access tokens based on the requested scopes.
docs update · Aug 2026
· source
-
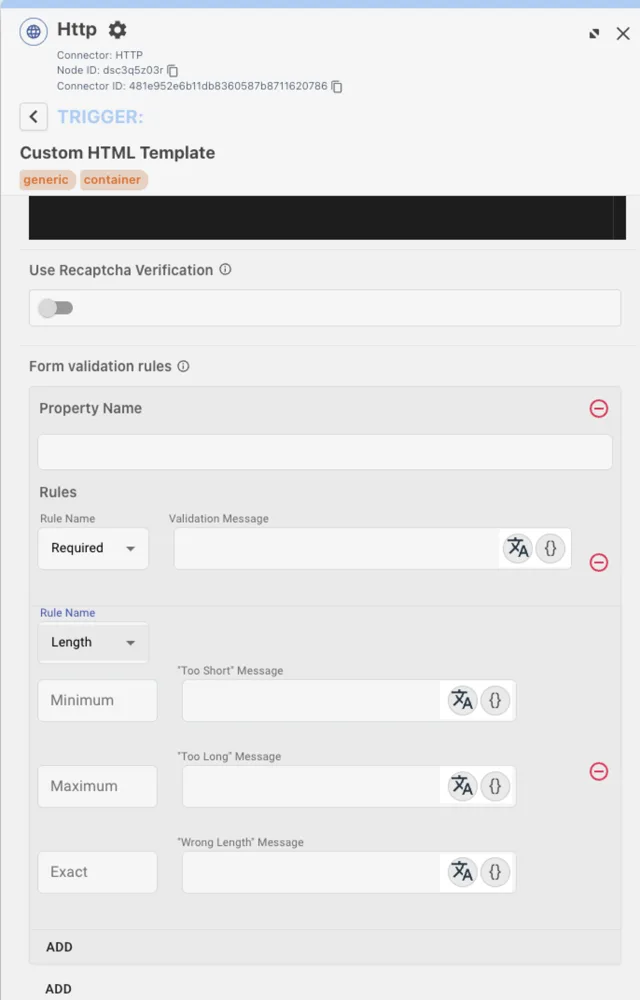
August 11 Attribute mapping for custom resource scopes You can now map attributes to scopes defined for a custom resource. This capability allows you to control which attributes are included in access tokens based on the requested scopes.
 docs update · Aug 2026
· source
Promotions API report metadata ordering shipped The promotions API returns report metadata sorted by creation date with the most recent entries first.
release 7 total
-
Adds
runTargetPhaseselection in the Advanced Identity Cloud admin console when running reconciliations.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ changelog · Oct 2026 · source · release history -
Adds
runTargetPhaseselection in the Advanced Identity Cloud admin console when running reconciliations.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history - The promotions API now returns report metadata ordered by creation date, most recent first (FRAAS-33591). changelog · Aug 2026 · source · release history
- The promotions API now returns report metadata ordered by creation date, most recent first. changelog · Jul 2026 · source · release history
- Promotions API now returns report metadata ordered by creation date, most recent first. 16 Jul 2026 (2026-07-17) · Jul 2026 · source · release history
- The promotions API now returns report metadata ordered by creation date, with the most recent first 16 Jul 2026 · Jul 2026 · source · release history
Combined/OATH/Push Registration JS disablement shipped A useJavaScript option allows rendering QR codes without client-side JavaScript for Combined MFA, OATH, and Push Registration nodes.
release
- Adds an option to the Combined MFA Registration, OATH Registration, and Push Registration nodes to render QR codes without using JavaScript. changelog · Sep 2026 · source · release history
- Adds an option to the Combined MFA Registration, OATH Registration, and Push Registration nodes to render QR codes without requiring JavaScript. changelog · Sep 2026 · source · release history
- Combined MFA Registration, OATH Registration, and Push Registration nodes now include an option to render QR codes without JavaScript. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
-
config: Adds theuseJavaScriptoption (default false) to Combined MFA Registration, OATH Registration, and Push Registration nodes to render QR codes without client-side JavaScript 02 Sep 2026 · Sep 2026 · source · release history
docs
- September 2026 02 Sep 2026 Version 23453.0 IAM-9603: The Combined MFA Registration, OATH Registration, and Push Registration nodes now include an option to render QR codes without using JavaScript. changelog · Sep 2026 · source
example
-
Present MFA enrollment QR codes to users in environments that block JavaScript (e.g., hardened kiosk browsers) by disabling JS rendering in registration nodes.
In the journey editor, select the 'Push Registration', 'OATH Registration', or 'Combined MFA Registration' node, open its properties, and enable the option 'Render QR code without JavaScript'.changelog · Sep 2026 · source -
Render QR codes server-side for accessibility or headless testing without requiring client JS.
<Journey JSON snippet> 'nodeId': 'mfa-qr', 'nodeType': 'CombinedMFANode', 'useJavaScript': false </Journey JSON snippet>02 Sep 2026 · Sep 2026 · source
ESV secret storage identifier update shipped ESV secrets in Google Secret Manager now use a unique name-and-version identifier by default, with an option to retain legacy stable ID behavior.
release
-
Adds
esv.am.secrets.gsm.stableid.version.onlyenvironment variable to retain legacy Google Secret Manager JWKkidbehavior when ESV secrets would otherwise use the new unique name-and-version identifier. changelog · Sep 2026 · source · release history -
ESV secrets are now stored in Google Secret Manager using a unique name-and-version identifier as the default JWK
kid; deployments where multiple secrets shared the same GSM version must setesv.am.secrets.gsm.stableid.version.onlyto retain the legacykidvalue. changelog · Sep 2026 · source · release history -
Adds
esv.am.secrets.gsm.stableid.version.onlyenvironment variable to control Google Secret Manager stable ID behavior for ESV secrets. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history -
The default JWK kid for ESV secrets stored in Google Secret Manager now uses a unique name-and-version identifier, which changes behavior from previous versions; set
esv.am.secrets.gsm.stableid.version.onlyto true to retain legacy stable ID behavior. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history -
ESV secrets in Google Secret Manager now default to a unique name-and-version identifier as the JWK
kid; installations relying on the legacy GSM-version-onlykidmust set theesv.am.secrets.gsm.stableid.version.onlyenvironment variable totrueto preserve prior behavior. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history -
esv.am.secrets.gsm.stableid.version.onlyenvironment variable must be set to true to retain legacy ESV secret behavior; otherwise, secrets are stored using a unique name-and-version identifier in Google Secret Manager (GSM) 02 Sep 2026 · Sep 2026 · source · release history
example
-
Retain legacy stable ID behavior for existing Google Secret Manager integrations.
export esv.am.secrets.gsm.stableid.version.only=true02 Sep 2026 (2026-09-03) · Sep 2026 · source
Multi-select list properties in custom scripted nodes shipped Custom scripted nodes can present users or administrators with a multi-select list of options as a configuration property.
release
- Adds callbacksBuilder.qrCodeCallback() binding to scripted nodes, enabling QR codes to render in the Advanced Identity Cloud admin console.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ 22 Oct 2026 (2026-10-23) · Oct 2026 · source · release history
- Adds multi-value selection from predefined options when configuring custom node properties in the node designer. changelog · Oct 2026 · source · release history
- Adds the ability to select multiple values from predefined options when configuring custom node properties in the node designer. changelog · Oct 2026 · source · release history
- Allows selection of multiple values from predefined options when configuring custom node properties in the node designer. 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history
-
Custom scripted nodes now support combining
multivalued: truewithoptionsto create multi-select list properties in the journey designer. 21 Jul 2026 (2026-07-22) · Jul 2026 · source · release history
example
-
Generate a QR code inside a scripted authentication node to display to users in the admin console.
callbacksBuilder.qrCodeCallback()22 Oct 2026 (2026-10-23) · Oct 2026 · source
Hosted account pages navigation profiles shipped Navigation profiles can be assigned to user groups to serve tailored navigation menus on hosted account pages.
release
- Adds customizable hosted account pages navigation menu via navigation profiles, enabling different menus for different groups of users. changelog · Oct 2026 · source · release history
- Adds navigation profiles to customize the hosted account pages navigation menu for different groups of users. changelog · Oct 2026 · source · release history
- Enables customization of the hosted account pages navigation menu for different user groups using navigation profiles. 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history
- Adds navigation profiles to customize hosted account page menus for different user groups 28 Sep 2026 · Sep 2026 · source · release history
example
-
Tailor the hosted account portal menu so that, for example, admin-tier users see account management links that standard users do not.
In the admin console, go to Hosted Pages > Navigation Profiles, create a new profile, assign it to the target user group, and configure the menu items to expose.changelog · Oct 2026 · source -
Serve tailored navigation menus to different user groups on hosted account pages by assigning navigation profiles per group.
In the Advanced Identity Cloud admin console, go to Hosted Pages > Navigation Profiles, create a profile for a user group, define the menu items, then assign the profile to the target group.28 Sep 2026 (2026-09-29) · Sep 2026 · source
Next-generation scripting engine as default shipped The next-generation scripting engine is the default and recommended option when creating scripts in the admin console.
release
- Makes the next-generation scripting engine the default when creating scripts in the Advanced Identity Cloud admin console. changelog · Oct 2026 · source · release history
- Makes the next-generation scripting engine the default and recommended option when creating scripts in the Advanced Identity Cloud admin console. changelog · Oct 2026 · source · release history
- Makes the next-generation scripting engine the default and recommended option when creating scripts in the Advanced Identity Cloud admin console. 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history
- Makes the next-generation scripting engine the default and recommended option for script creation in the Advanced Identity Cloud admin console (OPENAM-28382) 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history
- Next-generation scripts include utils.base64url.encode() and utils.base64url.decodeToBytes() for Base64URL encoding/decoding 24 Mar 2026 · Mar 2026 · source · release history
- Added identity.exists() method to next-generation objects returned by idRepository.getIdentity() 13 Feb 2026 · Feb 2026 · source · release history
PingOne Worker service credential-based connection toggle shipped A toggle on the PingOne Worker service automatically shows or hides the relevant connection fields depending on whether credential-based connection is selected.
release
- Adds Store Software Statement setting on the OAuth 2.0 provider to persist the software statement provided during dynamic client registration (DCR) in the client configuration and return it in DCR read responses. 14 Sep 2026 (2026-09-15) · Sep 2026 · source · release history
- The Enable Connection via Credential toggle for the PingOne Worker service now automatically enables or disables relevant connection fields based on selection. 21 Jul 2026 (2026-07-22) · Jul 2026 · source · release history
- The PingOne worker service now lets you configure the connection to PingOne using a credential JWT. 04 Jun 2026 (2026-06-05) · Jun 2026 · source · release history
- PingOne Worker Service connection can now be configured using a credential JWT (AME-33973) 24 Mar 2026 · Mar 2026 · source · release history
example
-
Preserve DCR software statements in client configs so they are returned in read responses — useful for auditing which software statement a dynamically registered client used.
In the admin console, go to Native Consoles > Access Management > Realms > <realm> > Services > OAuth2 Provider > Dynamic Registration, and enable 'Store Software Statement in OAuth2 Client'.changelog · Sep 2026 · source -
Preserve software statements across DCR lifecycle calls so downstream systems can audit the original client assertion on every read response.
In the Advanced Identity Cloud admin console, go to Native Consoles > Access Management > Services > OAuth 2.0 Provider, then enable the 'Store Software Statement in OAuth2 Client' setting and save.14 Sep 2026 (2026-09-15) · Sep 2026 · source
DaVinci administrative audit events shipped Administrative actions taken in DaVinci are recorded as audit events, giving operators a reliable record of who did what.
Also counts toward: Administrative audit log
release
-
config: Adds theuseJavaScriptoption (default false) to Combined MFA Registration, OATH Registration, and Push Registration nodes to render QR codes without client-side JavaScript 02 Sep 2026 · Sep 2026 · source · release history -
Expanded monitoring search feature to include
/payload/messageand/payloadfields. 14 Apr 2026 · Apr 2026 · source · release history -
Adds
jaslog source for monitoring Java API Service (JAS) identity management audit messages 09 Apr 2026 · Apr 2026 · source · release history -
Adds
iga-apilog source for monitoring Identity Governance API events, certifications, SOD, glossary, and LCM 09 Apr 2026 · Apr 2026 · source · release history
docs
-
DaVinci audit events released for general availability We’ve released DaVinci administrative audit events for general availability. You can find them listed in DaVinci administrative audit events July 30 HubSpot provisioning connection You can now provision users and groups between your HubSpot account and PingOne.
docs update · Jul 2026
· source
-
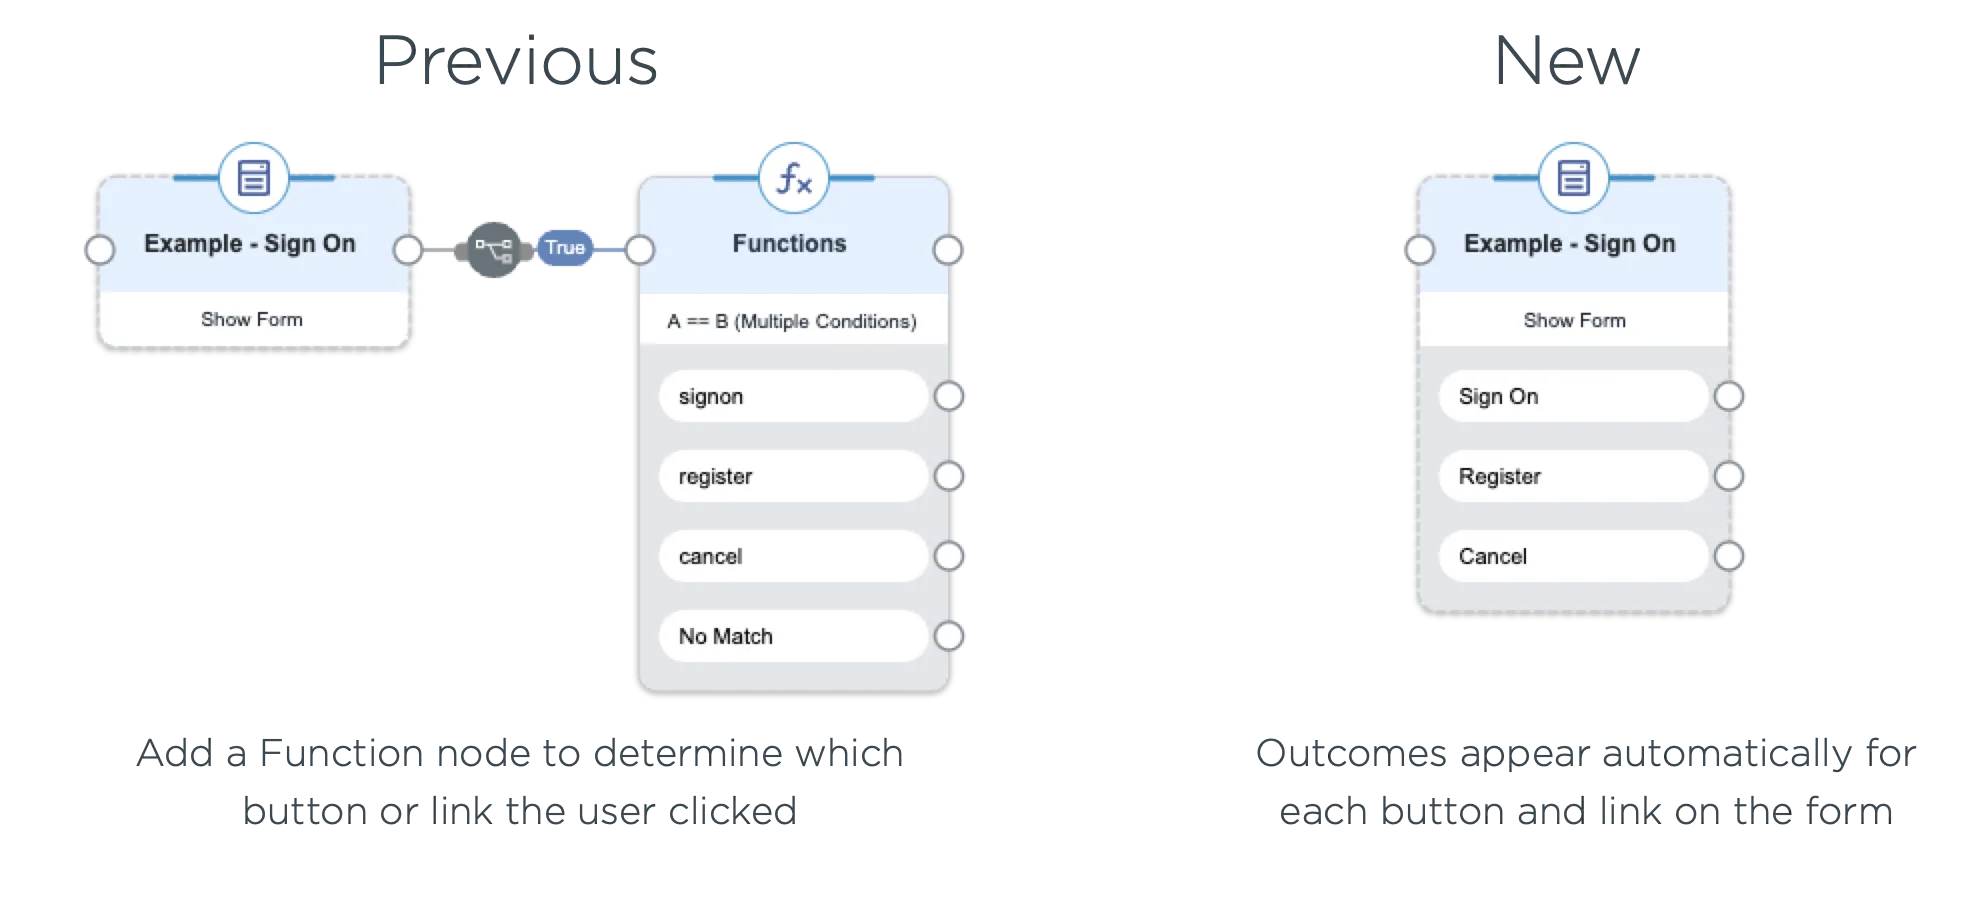
New features and improvements in PingOne DaVinci. Updated July 30, 2026. July 31 DaVinci audit events released for general availability We’ve released DaVinci administrative audit events for general availability.
 docs update · Jul 2026
· source
MFA and device binding integrations shipped The cyber tooling supports extended configurations for RSA SecurID, PingOne Verify, PingOne Protect, and WebAuthn nodes, including device clock skew tolerance and conditional UI passkey autofill.
Also counts toward: Multi-factor authentication
release
- PingOne Protect Initialize node gains Additional Signals SDK Initialization Options attribute for extended configuration 18 Mar 2026 · Mar 2026 · source · release history
-
PingOneProtectInitializeCallback introduces
universalDeviceIdentificationfield replacing deprecatedenableTrust18 Mar 2026 · Mar 2026 · source · release history - Device Binding and Device Signing Verifier nodes allow specifying clock skew between client device and AIC 13 Feb 2026 · Feb 2026 · source · release history
- PingOne Verify Evaluation node gains a property to enable automatic redirection after verification in Redirect delivery mode 13 Feb 2026 · Feb 2026 · source · release history
- New RSA SecurID node replaces the deprecated Marketplace RSA SecurID node 13 Feb 2026 · Feb 2026 · source · release history
docs
-
September 24 NFC verification from PingOne Verify available for early access NFC Verification is now available for early access. This capability lets users use near-field communication (NFC) verification on their mobile device to read a secure NFC chip on their government-issued ID or passport.
seen Sep 2026
· source
Telephone number user property format shipped User properties can be formatted as telephone numbers, with optional server-side validation and separate country code and phone number fields in hosted pages and the admin console.
Also counts toward: Web management console
release
-
Adds
telephone numberas a user property format with optional server-side validation, providing separate country code and phone number fields in hosted pages and the admin console. changelog · Oct 2026 · source · release history - Adds telephone number as a user property format, with optional server-side validation and separate country code and phone number fields in hosted pages and the admin console. changelog · Oct 2026 · source · release history
-
Adds
telephonenumber as a selectable User property format with optional server-side validation and separate country code/phone fields in hosted pages and the admin console (IAM-2187) 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history - Supports telephone number as a user property format, with optional server-side validation and separate country code and phone number fields in journeys. 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history
docs
- 28 Sep 2026 Versions 23852.0, 23861.0 AME-35111: The node designer now lets you select multiple values from predefined options when configuring custom node properties. IAM-2187: User properties now let you choose telephone number as a property format, with optional server-side validation. changelog · Oct 2026 · source
LexisNexis DDP node naming and response storage shipped ThreatMetrix nodes are renamed to LexisNexis Dynamic Decision Platform (DDP) nodes, and LexisNexis InstantID Question and Answer nodes now store decision API responses in shared state.
release
- ThreatMetrix nodes are renamed to LexisNexis Dynamic Decision Platform (DDP) nodes — any journeys or configurations referencing the old ThreatMetrix node names will need to be updated. changelog · Oct 2026 · source · release history
- ThreatMetrix nodes have been renamed to LexisNexis Dynamic Decision Platform (DDP) nodes — any configuration or documentation referencing the old ThreatMetrix node names will need to be updated. changelog · Oct 2026 · source · release history
- Renames ThreatMetrix nodes to LexisNexis Dynamic Decision Platform (DDP) nodes; updates LexisNexis InstantID Question and Answer (IIDQA) nodes to store decision API responses in shared state. changelog · Oct 2026 · source · release history
- Renames ThreatMetrix nodes to LexisNexis Dynamic Decision Platform (DDP) nodes, and updates LexisNexis InstantID Question and Answer (IIDQA) nodes to store decision API responses in shared state. changelog · Sep 2026 · source · release history
docs
- 21 Sep 2026 Versions 23688.0, 23706.0 TNTP-278: The ThreatMetrix nodes have been renamed to LexisNexis Dynamic Decision Platform (DDP) nodes. The LexisNexis InstantID Question and Answer (IIDQA) nodes have been updated to store the decision API responses in shared state. changelog · Sep 2026 · source
Reconciliation phase targeting shipped A specific phase of a reconciliation run can be selected via runTargetPhase, enabling partial-sync execution and debugging of individual reconciliation phases.
Also counts toward: Web management console
release
-
Allows selecting
runTargetPhasewhen running reconciliations from the Advanced Identity Cloud admin console (IAM-11060) 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history -
Adds
runTargetPhaseselection in the admin console to control reconciliation execution phases 28 Sep 2026 · Sep 2026 · source · release history - Adds ability to cancel a clustered reconciliation even when a route associated with the source or target system is unavailable (OPENIDM-21493) 06 Feb 2026 · Feb 2026 · source · release history
- Switches Advanced Identity Cloud identity management service to use synchronous HTTP client requests for external connections, preventing connection closure exceptions from terminating reconciliation 06 Feb 2026 · Feb 2026 · source · release history
example
-
Select
runTargetPhaseduring a reconciliation run to control which phase of the reconciliation executes — useful for debugging or partial-sync scenarios.In the Advanced Identity Cloud admin console, open Reconciliations, select a reconciliation configuration, click 'Run', and choose `runTargetPhase` from the phase options before confirming.changelog · Oct 2026 · source
Connector server name ESV support shipped Administrators can use environment secrets or variables to specify the connector server name in the connector configuration modal.
release
- Supports using an ESV (environment secret/variable) for the connector server name in connector configuration.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ changelog · Sep 2026 · source · release history
- Enables use of an ESV (Environment Secret/Variable) for the connector server name in the New Connector Server modal. changelog · Aug 2026 · source · release history
- Adds support for using an ESV to specify the connector server name within the New Connector Server modal 18 Aug 2026 (2026-08-19) · Aug 2026 · source · release history
- Enables use of an ESV for the connector server name in the New Connector Server modal. 18 Aug 2026 (2026-08-19) · Aug 2026 · source · release history
-
Enables reuse of
environment ESVCs(ESVC) values for the connector server name in the New Connector Server modal. 18 Aug 2026 · Aug 2026 · source · release history
IGA Role Lifecycle Management enhancements shipped Designated end users can create, update, and delete roles via workflow-driven requests, with read-only membership views and individual grant/removal submissions.
release
- IGA now enforces the required request justification setting consistently across lifecycle management, request extension, and entitlement-grant requests. changelog · Sep 2026 · source · release history
- IGA role request forms now display current role membership as read-only, and each member addition or removal in the role lifecycle management screen is submitted as an individual grant or removal request. changelog · Sep 2026 · source · release history
- IGA role request forms display current role membership as read-only; each member addition or removal in the role lifecycle management screen is submitted as an individual grant or removal request. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
- Identity Governance role LCM (IGA-4265): Allows designated end users to create, update, and delete roles on behalf of others via workflow-driven requests without full admin access. 04 Jun 2026 (2026-06-05) · Jun 2026 · source · release history
- Introduces role lifecycle management (LCM) allowing end users to create, update, and delete roles via workflow-driven requests. 04 Jun 2026 · Jun 2026 · source · release history
Email delivery from journey scripts shipped Scripts running inside journeys can send emails directly without needing a separate integration.
release
- Adds the ability to send email from next-generation scripts. changelog · Aug 2026 · source · release history
-
Adds
emailServicebinding for next-generation scripts, enabling email delivery directly from journey scripts. changelog · Jul 2026 · source · release history -
Advanced Identity Cloud now provides a
emailServicenext-generation script binding that lets you send email directly from a script. 21 Jul 2026 (2026-07-22) · Jul 2026 · source · release history -
Adds the
emailServicenext-generation script binding to send email directly from scripts 21 Jul 2026 · Jul 2026 · source · release history
docs
- 22 Jul 2026 Versions 22875.0, 22883.0 21 Jul 2026 Versions 22832.0, 22855.0 Send email from next-generation scripts (OPENAM-25617) Advanced Identity Cloud now provides a next-generation script binding, emailService , that lets you send email directly from a script. changelog · Jul 2026 · source
Multi-line formatting in journey annotation notes shipped Multi-line text entered in journey annotation notes is displayed correctly when the journey is viewed, not just while editing.
release
- Journey annotation notes now display multi-line formatting in view mode. changelog · Jul 2026 · source · release history
- Journey annotation notes now render multi-line formatting in view mode, consistent with edit mode. 16 Jul 2026 (2026-07-17) · Jul 2026 · source · release history
- Journey annotation notes in the admin console display multi-line formatting in view mode 16 Jul 2026 (2026-07-17) · Jul 2026 · source · release history
-
Adds the
esv-global-saml-error-page-http-bindingenvironment variable to override the HTTP binding (HTTP-POST or HTTP-Redirect) used for SAML error page redirects 18 Feb 2026 · Feb 2026 · source · release history
example
-
View journey annotations with preserved multi-line formatting in the admin console.
Open a journey in the Advanced Identity Cloud admin console and switch to 'view mode' for annotation notes.16 Jul 2026 (2026-07-17) · Jul 2026 · source
Advanced Identity Cloud node versioning shipped Node versions are supported with version-aware API endpoints for Page, Username, WebAuthn Authentication, and WebAuthn Registration nodes.
Also counts toward: REST API
release
- Advanced Identity Cloud supports node versioning with new versions for Page, Username, WebAuthn Authentication, and WebAuthn Registration nodes. 04 Jun 2026 (2026-06-05) · Jun 2026 · source · release history
-
Versionless node endpoints are deprecated; the
realm-config/authentication/authenticationtrees/nodesURL must specify the node version (e.g.,/nodes/UsernameCollectorNode/2.0). 04 Jun 2026 · Jun 2026 · source · release history -
Adds node versioning support for Username,
WebAuthn Authentication, andWebAuthn Registrationnodes with version-aware API endpoints. 04 Jun 2026 · Jun 2026 · source · release history
example
-
Configure node versioning for authentication trees via the API.
curl -X PUT 'https://<tenant-env-fqdn>/am/json/realms/root/realms/alpha/realm-config/authentication/authenticationtrees/nodes/UsernameCollectorNode/2.0' -H 'Accept-API-Version:…04 Jun 2026 (2026-06-05) · Jun 2026 · source -
Configure a version-aware request to retrieve Username nodes.
curl -H 'Accept-API-Version: protocol=2.1,resource=3.0' https://<tenant-env-fqdn>/am/json/realms/root/realm-config/authentication/authenticationtrees/nodes/UsernameCollectorNode/2.004 Jun 2026 · Jun 2026 · source
Authentication journey node configuration and management shipped Journey designers can retrieve node definitions programmatically, configure backchannel retry and real-time notification behaviors, and set custom headers on journey success, failure, and error outcomes.
release
- Backchannel Notification node sends real-time status updates from a backchannel journey to the main auth journey 18 Mar 2026 · Mar 2026 · source · release history
- Backchannel Initialize node gains an Allow Retry option for end users to retry failed backchannel authentication journeys 13 Feb 2026 · Feb 2026 · source · release history
- Set Success Details, Set Failure Details, and Set Error Details nodes now support setting custom headers on journey outcomes 13 Feb 2026 · Feb 2026 · source · release history
- New JWT Password Replay node secures the user’s password within an encrypted JWT for PingGateway 13 Feb 2026 · Feb 2026 · source · release history
example
-
Retrieve the latest node definitions for all authentication tree nodes in a single call
curl -X GET 'https://<aic-host>/idp/rest/realm-config/authentication/authenticationtrees/nodes?action=listLatestNodeDefinitions' -H 'Authorization: Bearer <token>'13 Feb 2026 · Feb 2026 · source
Advanced Reporting username resolution for entitlement reviews shipped Advanced Reporting returns usernames instead of GUIDs for the `Completed By` field in entitlement review items.
release
-
Reports have been improved: several parameters in built-in reports are now optional, allowing reports to run with broader criteria, and in custom reports the Completed By field in the Entitlement Review Item entity now returns the
userNamevalue. changelog · Oct 2026 · source · release history -
Custom reports: the Completed By field in the Entitlement Review Item entity now returns the
userNamevalue, and several parameters in built-in reports are now optional, allowing reports to be run with broader criteria. 22 Oct 2026 (2026-10-23) · Oct 2026 · source · release history - In Advanced Reporting, the Completed By field in entitlement review items now returns usernames instead of GUIDs. 15 Oct 2026 (2026-10-15) · Oct 2026 · source · release history
- The Completed By field in entitlement review items now returns usernames instead of GUIDs — saved reports or integrations that expect GUIDs must be updated. 15 Oct 2026 (2026-10-15) · Oct 2026 · source · release history
LexisNexis DDP Profiler node script injection configuration shipped The LexisNexis DDP Profiler node can be configured to inject scripts in the head element or in an iframe.
release
-
Adds configuration option to the LexisNexis DDP Profiler node to inject scripts in the
headelement or in an iframe. changelog · Oct 2026 · source · release history -
Allows configuring the LexisNexis DDP Profiler node to inject scripts in the
headelement or in an iframe. 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history - Adds LexisNexis DDP Profiler node capability to inject scripts in head or iframe elements 28 Sep 2026 · Sep 2026 · source · release history
example
-
Configure a LexisNexis DDP Profiler node to inject scripts into an iframe.
// In the journey designer, select the LexisNexis DDP Profiler node and configure injection location: 'iframe'28 Sep 2026 · Sep 2026 · source
Self-service journey mapping configuration in admin console shipped Administrators can configure self-service journey mappings directly in the admin console rather than through an API.
Also counts toward: Web management console
release
- Adds multi-node selection on journey canvases by holding Shift and clicking each node. changelog · Oct 2026 · source · release history
- Self-service journey mappings can now be configured directly in the Advanced Identity Cloud admin console. changelog · Jul 2026 · source · release history
- Supports configuring self-service journey mappings directly in the Advanced Identity Cloud admin console. 08 Jul 2026 (2026-07-09) · Jul 2026 · source · release history
- Configure self-service journey mappings directly in the Advanced Identity Cloud admin console 08 Jul 2026 · Jul 2026 · source · release history
ESV-backed email provider 'from' address shipped The 'from' address for email providers can be set using an environment secret or variable rather than a hardcoded value.
release
-
Adds
userAgentproperty to external REST service configuration, defaulting toPingIdentityfor outbound requests, overridable per-request.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ changelog · Sep 2026 · source · release history - Supports using an environment secret or variable (ESV) to configure the from address for email providers. 08 Jul 2026 (2026-07-09) · Jul 2026 · source · release history
example
-
Override the default outbound user agent for a specific external REST service call by setting the
userAgentproperty, useful when a third-party API enforces a particular User-Agent string.{ "userAgent": "MyCompanyIntegration/1.0" }changelog · Sep 2026 · source -
Use an ESV to centrally manage and rotate the from address for email providers without hardcoding values in the console.
In the admin console, go to Email Provider settings, and set the 'From Address' field to an ESV reference (e.g., &esv.email.from.address).08 Jul 2026 (2026-07-09) · Jul 2026 · source
Friendly CAPTCHA provider support for CAPTCHA node v2 shipped The v2.0 CAPTCHA node supports Friendly Captcha as a privacy-focused CAPTCHA provider alternative.
release
- Adds Friendly Captcha support to the v2.0 CAPTCHA node as a privacy-focused CAPTCHA provider alternative. changelog · Sep 2026 · source · release history
- Adds support for Friendly Captcha to the v2 CAPTCHA node as a privacy-focused CAPTCHA provider alternative. changelog · Sep 2026 · source · release history
- Adds Friendly Captcha support to the v2 CAPTCHA node as a privacy-focused CAPTCHA provider alternative. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
- new: v2.0 CAPTCHA node adds support for Friendly Captcha as a privacy-focused provider 02 Sep 2026 · Sep 2026 · source · release history
Managed user update conflict resolution shipped Managed user updates that conflict with generated attribute values are now accepted and propagate to all associated workforce application accounts.
release
- Enables updating a managed user even when the change conflicts with generated attribute values, propagating updates to all associated workforce application accounts during queued synchronization. changelog · Sep 2026 · source · release history
- Enables updating a managed user even when the change conflicts with generated attribute values, propagating the update to all associated workforce application accounts during queued synchronization. changelog · Sep 2026 · source · release history
- Managed user updates that conflict with generated attribute values are now accepted and propagate to all associated workforce application accounts during queued synchronization. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
- config: You can now update a managed user even when the change conflicts with generated attribute values, propagating to all associated workforce application accounts during queued synchronization 02 Sep 2026 · Sep 2026 · source · release history
Script error visibility for ESVs shipped The script editor surfaces error messages when scripts reference environment secrets or variables incorrectly.
release
- Shows errors in the script editor when scripts use environment ESVs incorrectly. changelog · Sep 2026 · source · release history
- Surfaces script errors directly in the script editor when scripts reference environment ESVs incorrectly. changelog · Aug 2026 · source · release history
- Surfaces errors in the script editor when scripts reference environment ESVs incorrectly. 18 Aug 2026 (2026-08-19) · Aug 2026 · source · release history
- Adds visibility of script error messages when environment variables (ESVs) are used incorrectly in scripts 18 Aug 2026 (2026-08-19) · Aug 2026 · source · release history
Sequential identity creation in admin console shipped Administrators can create multiple identities sequentially without closing the creation modal, improving workflow efficiency.
release
- Allows creating another identity immediately after creating one, without closing the modal. changelog · Aug 2026 · source · release history
- Allows creating another identity immediately after creating one, without closing the modal. 18 Aug 2026 (2026-08-19) · Aug 2026 · source · release history
- Adds ability to create multiple identities sequentially without closing the modal window 18 Aug 2026 (2026-08-19) · Aug 2026 · source · release history
- Allows sequential identity creation without closing the modal, improving workflow efficiency. 18 Aug 2026 · Aug 2026 · source · release history
Patch Object node v2.0 shipped The Patch Object node now consistently updates managed identity objects as Advanced Identity Cloud, replacing the older behaviour.
release
- Adds v2.0 of the Patch Object node in Advanced Identity Cloud journey flows (OPENAM-26073). changelog · Aug 2026 · source · release history
- Introduces Patch Object node v2.0, which always updates managed identity objects as Advanced Identity Cloud (v1.0 deprecated but still functional). changelog · Jul 2026 · source · release history
- The Patch as Object configuration option is removed from the v2.0 Patch Object node; it now always updates the managed identity object as Advanced Identity Cloud. 20 Jul 2026 (2026-07-21) · Jul 2026 · source · release history
- New v2.0 of the Patch Object node always updates the managed identity object as Advanced Identity Cloud, removing the Patch as Object configuration option (v1.0 is deprecated but remains functional in existing journeys). 20 Jul 2026 (2026-07-21) · Jul 2026 · source · release history
Proxy Connect configuration in admin console shipped Tenants using Proxy Connect can manage that configuration in the admin console rather than calling the API directly.
Also counts toward: Web management console
release
- Proxy Connect enabled tenants can now manage Proxy Connect configuration directly in the Advanced Identity Cloud admin console without using the API. changelog · Jul 2026 · source · release history
- Allows Proxy Connect–enabled tenants to manage Proxy Connect configuration directly in the admin console without using the API. 08 Jul 2026 (2026-07-09) · Jul 2026 · source · release history
- Manage Proxy Connect configuration directly in the Advanced Identity Cloud admin console without using the API 08 Jul 2026 · Jul 2026 · source · release history
example
-
Manage Proxy Connect configuration through the UI instead of making API calls — useful for tenants who want to avoid direct API access for routine config changes.
In the admin console, go to Settings > Proxy Connect and update your Proxy Connect configuration directly in the panel.08 Jul 2026 (2026-07-09) · Jul 2026 · source
Social identity provider management in admin console shipped Social identity providers can be created and edited directly in the admin console without writing API calls.
Also counts toward: Web management console
release
- Social identity providers can now be created and edited directly in the Advanced Identity Cloud admin console. changelog · Jul 2026 · source · release history
- Enables creation and editing of social identity providers directly in the Advanced Identity Cloud admin console. 08 Jul 2026 (2026-07-09) · Jul 2026 · source · release history
- Create and edit social identity providers in the Advanced Identity Cloud admin console 08 Jul 2026 · Jul 2026 · source · release history
example
-
Create or edit a social identity provider entirely within the admin console, avoiding manual API calls.
In the admin console, go to Identities > Social Identity Providers, then select Create Provider or edit an existing one.08 Jul 2026 (2026-07-09) · Jul 2026 · source
Secret mapping validation shipped Operators can test that a secret mapping resolves correctly against the configured secret store before relying on it.
Also counts toward: REST API
release
-
New
validateaction on the secrets endpoint lets operators confirm whether a secret mapping resolves to a valid secret in the configured secret store. 21 Jul 2026 (2026-07-22) · Jul 2026 · source · release history -
You can now use a new
validateaction on the secrets endpoint to validate whether a secret mapping resolves to a valid secret in the configured secret store. 21 Jul 2026 (2026-07-22) · Jul 2026 · source · release history -
Adds a new
validateaction on the secrets endpoint to check if a secret mapping resolves correctly 21 Jul 2026 · Jul 2026 · source · release history
example
-
Validate that a secret mapping resolves correctly in the configured secret store before relying on it in production.
curl -X POST \ 'https://<tenant>.forgeblocks.com/am/json/realms/root/realm-config/secrets/stores/<store-id>/mappings/<mapping-id>?_action=validate' \ -H 'Authorization: Bearer <access-token>' \ -H…21 Jul 2026 (2026-07-22) · Jul 2026 · source
OAuth 2.0 AME scripting engine support shipped OAuth 2.0 AME scripts including OIDC claims, Scripted JWT validator, and Scope validation can now use the next-generation scripting engine.
Also counts toward: JavaScript scripting support, Scripting API, Scripting language support
release
-
New
scopeValidatorHelperbinding with inheritAccessTokenScopesOnRefresh() method in next-generation OAuth 2.0 scope validation scripts 24 Mar 2026 · Mar 2026 · source · release history -
Next-generation OAuth 2.0 scope validation scripts gain access to the
availableScopesbinding and throwInvalidScope() method 24 Mar 2026 · Mar 2026 · source · release history -
jwtValidatorandjwtAssertionbindings are available in all next-generation scripts for scripted JWT operations 24 Mar 2026 · Mar 2026 · source · release history -
OAuth 2.0 AME scripts (OIDC claims, Scripted JWT validator, Scope validation, Authorize endpoint data provider, Scope evaluation, May act) can now use the next-generation scripting engine with
utilsandopenidmbindings 13 Feb 2026 · Feb 2026 · source · release history
Managed object enum value case normalisation shipped Managed object enum values are automatically rewritten to the exact case defined in the schema on create, update, or patch operations.
release
- Managed object enum-typed properties are now matched and rewritten without regard to case, normalizing submitted values to the exact case defined in the schema. changelog · Oct 2026 · source · release history
-
Managed object enum values are now normalized to schema-defined case on write — scripts or dashboards that compare
accountStatusor other enum property values against non-canonical cases (e.g. Active instead of active) must be updated to expect the exact case defined in the schema. changelog · Oct 2026 · source · release history - Managed object enum values are now rewritten to the exact schema-defined case on create, update, or patch (e.g. Active becomes active if the schema defines active). Scripts or dashboards that compare enum property values using non-schema case will need to be updated to expect the schema-defined case. 22 Oct 2026 (2026-10-23) · Oct 2026 · source · release history
Relational integrity enforcement shipped The system now rejects relationship creation requests that reference a property not accepting the given object type, rather than silently routing them.
release
- The underlying datastore now enforces unique usernames and application names. 22 Oct 2026 (2026-10-23) · Oct 2026 · source · release history
- Advanced Identity Cloud now rejects relationship creation requests that use a property not accepting the referenced object type; previously these were silently created via a different valid property. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
- Advanced Identity Cloud now rejects relationship creation requests that reference a property not accepting the given object type, rather than silently routing through a different property. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
OAuth 2.0 request state stored in CTS shipped OAuth 2.0 request state is held server-side rather than in a browser cookie, preventing failures when request data is large.
release
- Backchannel transactions now record the authenticated subject on completion even when no session is created, preserving a subject declared before authentication. changelog · Oct 2026 · source · release history
- Adds Authentication Request Storage option on the hosted IdP to configure where SAML authentication requests are stored, enabling concurrent SAML SSO attempts across multiple browser tabs or browsers to complete independently. 14 Sep 2026 (2026-09-15) · Sep 2026 · source · release history
-
OAuth 2.0 request state is now stored in CTS (Core Token Service) instead of an oversized browser cookie, preventing large requests (e.g., with big
id_token_hint) from failing after authentication. changelog · Jul 2026 · source · release history
Federated administrator access with custom-domain redirect URI shipped Super administrators can specify a custom-domain redirect URI when configuring federated access for other administrators.
release
- Adds the ability in the v2.0 Choice Collector node to make choice callbacks with dynamically generated options that render as radio-button groups instead of drop-down lists. changelog · Sep 2026 · source · release history
- Super administrators can now configure the redirect URI to use a custom domain when setting up federated administrator access. changelog · Jul 2026 · source · release history
- Allows super administrators to configure a custom-domain redirect URI when setting up federated administrator access. 08 Jul 2026 (2026-07-09) · Jul 2026 · source · release history
Certificate chain validation enforcement shipped An ESV allows collecting the full certificate chain in Certificate Collector/Validation nodes, enforcing chain validation.
release
-
Adds
redirectUrlTypeandcustomRedirectUrlparameters to the backchannel transaction initialize endpoint, enabling customization of the redirect URI returned.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ 14 Sep 2026 (2026-09-15) · Sep 2026 · source · release history -
Backchannel transaction initialize endpoint accepts
redirectUrlTypeandcustomRedirectUrlparameters for customized redirect URI behavior. 14 Sep 2026 · Sep 2026 · source · release history -
New ESV
esv-am-nodes-certificatechain-validation-enforcedenables collecting the full certificate chain in Certificate Collector/Validation nodes 18 Mar 2026 · Mar 2026 · source · release history
Scheduled job start time override shipped Administrators can edit a scheduled job to start sooner than its originally configured future start time.
release
- Allows editing a scheduled job to start sooner than its originally configured future start time. changelog · Sep 2026 · source · release history
- Supports editing a future-scheduled job to start sooner. changelog · Aug 2026 · source · release history
- Enables editing a future-scheduled job to start sooner. 18 Aug 2026 (2026-08-19) · Aug 2026 · source · release history
IGA activity and notification monitoring GA shipped Identity governance provides general availability access to activity and notification monitoring with improved event type filtering and audit log presentation.
Also counts toward: Administrative audit log
release
- Adds IGA activity and notification monitoring as generally available, with event type filtering and audit log presentation. changelog · Sep 2026 · source · release history
- IGA activity and notification monitoring is now generally available, with improved event type filtering and audit log presentation. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
- new: IGA activity and notification monitoring is generally available with improved event type filtering and audit log presentation 02 Sep 2026 · Sep 2026 · source · release history
IGA workflow approval tasks with workflow variable expiration shipped Administrators can configure approval tasks in IGA workflows to be created when expiration is set using a workflow variable.
release
- Adds creation of approval tasks when expiration is configured with a workflow variable. changelog · Sep 2026 · source · release history
- Approval tasks can now be created when expiration is configured with a workflow variable. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
- config: Approval tasks can be created when expiration is configured with a workflow variable in IGA workflows 02 Sep 2026 · Sep 2026 · source · release history
Third-party SaaS provisioning connectors shipped Bundled connectors for applications like Snowflake enable centralized user, role, and data synchronization with the identity platform.
Also counts toward: Role-based access control
release
- Bundled Snowflake connector allows managing users, roles, and data sync between Advanced Identity Cloud and Snowflake. 14 Apr 2026 · Apr 2026 · source · release history
docs
-
Microsoft Entra ID provisioning connection You can now provision users and groups between your Microsoft Entra ID account and PingOne.
docs update · Aug 2026
· source
-
Microsoft Entra ID provisioning connection You can now provision users and groups between your Microsoft Entra ID account and PingOne.
docs update · Aug 2026
· source
PKCS5S2 password hash migration shipped User accounts with an outdated password hashing scheme can be upgraded to a stronger algorithm without disrupting access.
release
- Adds support for migrating user accounts from the deprecated PKCS5S2 password hashing scheme to a more secure algorithm (FRAAS-33086). changelog · Aug 2026 · source · release history
- Enables migration of user accounts from the deprecated PKCS5S2 password hashing scheme to a more secure algorithm. 08 Jul 2026 (2026-07-09) · Jul 2026 · source · release history
-
Migration of user accounts from deprecated
PKCS5S2password hashing to a more secure algorithm 08 Jul 2026 · Jul 2026 · source · release history
WebAuthn pubKeyCredParams sequence handling shipped When a WebAuthn credential is being created, the platform respects the order in which the client specifies its supported algorithm preferences.
release
-
Advanced Identity Cloud now honors the
pubKeyCredParamssequence in WebAuthn credential creation requests (OPENAM-25556). changelog · Aug 2026 · source · release history - Advanced Identity Cloud now supports the WebAuthn conditional UI (passkey autofill) in authentication nodes. 04 Jun 2026 (2026-06-05) · Jun 2026 · source · release history
- Adds support for WebAuthn conditional UI (passkey autofill) in the authentication journey nodes. 04 Jun 2026 · Jun 2026 · source · release history
AI Agents activation shipped Tenants where AI Agents has not yet been switched on can enable the feature directly from the AI Agents page in the admin console.
release
- Adds an Enable AI Agents button on the AI Agents page when the feature has not yet been activated. 08 Jul 2026 (2026-07-09) · Jul 2026 · source · release history
-
Adds
/environment/aiagent?_action=enableendpoint to simplify enabling AI Agents in sandbox environments 09 Apr 2026 · Apr 2026 · source · release history
example
-
Enable the AI Agents feature in a Ping Identity sandbox environment via API.
curl -X POST 'https://<pingone-env-id>/environment/aiagent?_action=enable' -H 'Authorization: Bearer <access_token>'09 Apr 2026 · Apr 2026 · source
SAML/OIDC application authorization policies shipped Authorization policies can be assigned to SAML or OIDC applications via IAM to restrict access to specific authenticated subsets.
release
- You can now assign an authorization policy to a SAML or OIDC application via IAM-4646 to restrict access to specific authenticated subsets. 04 Jun 2026 (2026-06-05) · Jun 2026 · source · release history
-
Enables assigning authorization policies to SAML or OIDC applications via the
IAM-9608enhancement. 04 Jun 2026 · Jun 2026 · source · release history
example
-
Restrict application access to a subset of users authenticated through a specific journey.
Assign an authorization policy to a SAML or OIDC application via IAM-464604 Jun 2026 (2026-06-05) · Jun 2026 · source
SAML remote identity provider alias import shipped Multiple remote identity providers sharing the same entity ID can be imported by specifying an alias, with uniqueness enforced per circle of trust.
release
- Ping Identity now lets you import multiple remote identity providers sharing the same entity ID by specifying an alias, with uniqueness enforced per circle of trust — aliased providers do not support single logout or Enhanced Client or Proxy (ECP), and hosted service-provider assertion consumer service URLs require a… changelog · Oct 2026 · source · release history
- Adds support for importing multiple remote identity providers sharing the same entity ID by specifying an alias; uniqueness is enforced per circle of trust. 22 Oct 2026 (2026-10-23) · Oct 2026 · source · release history
WS-Fed application service provider attribute name format shipped Custom WS-Fed applications support user-defined name formats for service provider attributes, allowing custom namespaces for relying party compatibility.
release
- Custom WS-Fed applications now support user-defined name formats for service provider attributes, letting you specify custom namespaces to meet the attribute requirements of specific relying parties. changelog · Oct 2026 · source · release history
- Custom WS-Fed applications now support user-defined name formats for service provider attributes, allowing custom namespaces for relying party compatibility. 22 Oct 2026 (2026-10-23) · Oct 2026 · source · release history
OAuth 2.0 Client ID Metadata Documents support shipped The cyber tool supports OAuth 2.0 Client ID Metadata Documents.
release
-
The OpenID Connect discovery endpoint now always returns
authorization_response_iss_parameter_supported: true, and authorization responses (including error responses) that redirect to the client now include theissparameter, enabling issuer verification. 22 Oct 2026 (2026-10-23) · Oct 2026 · source · release history - Supports OAuth 2.0 Client ID Metadata Documents (CIMD) 14 Sep 2026 (2026-09-15) · Sep 2026 · source · release history
Session token cookie persistence configuration documented Administrators can choose whether PingOne uses a persistent or non-persistent session token cookie for each environment.
docs
-
Session token cookie persistence You can now choose whether PingOne uses a persistent or non-persistent session token (ST) cookie for each environment. PingOne uses persistent ST cookies by default that remain in the browser until they expire or are removed.
docs update · Oct 2026
· source
-
Session token cookie persistence You can now choose whether PingOne uses a persistent or non-persistent session token (ST) cookie for each environment. PingOne uses persistent ST cookies by default that remain in the browser until they expire or are removed.
docs update · Oct 2026
· source
Journey canvas panning shipped Journey canvases can be panned by holding the space bar and dragging with the left mouse button.
release
- Improves journey canvas interactions by adding the ability to select multiple journey nodes by holding Shift and clicking each node, and to pan the canvas by holding the space bar and dragging with the left mouse button. changelog · Oct 2026 · source · release history
- Adds pan support for journey canvases by holding the space bar and dragging with the left mouse button. changelog · Oct 2026 · source · release history
PingID device removal after interrupted device change documented Administrators can remove PingID devices from the admin console in PingOne environments integrated with PingID, even after a device change was interrupted.
Also counts toward: Web management console
docs
-
October 2026 October 4 Improved removal of devices after interrupted device change TRIAGE-37308 We’ve fixed an issue that could prevent administrators from removing PingID devices from the PingOne admin console in certain PingOne environments integrated with PingID.
docs update · Oct 2026
· source
-
October 2026 October 4 Improved removal of devices after interrupted device change TRIAGE-37308 We’ve fixed an issue that could prevent administrators from removing PingID devices from the PingOne admin console in certain PingOne environments integrated with PingID.
docs update · Oct 2026
· source
PingID Workforce MFA capabilities in MFA Use Case Connector documented The MFA Use Case Connector supports additional PingID Workforce authentication capabilities, including a remember-me option for users.
Also counts toward: Multi-factor authentication
docs
-
New features and improvements in PingOne DaVinci. Updated October 5, 2026. October 2026 October 5 PingID Workforce capabilities added to the MFA Use Case Connector MFA Use Case Connector The MFA use case connector now supports the following PingID Workforce authentication capabilities: Remember me : Users who…
docs update · Oct 2026
· source
-
July 19 MFA API - changes to responses Changes have been made to the responses for API requests to get MFA user devices and to check if an MFA device is a remembered device. If you have code that depends upon the content of these responses, you might have to modify your code accordingly.
seen Jul 2026
· source
LDAP Decision node v2.0 and Identity Store Decision node v2.0 shipped Version 2.0 of the LDAP Decision node and the Identity Store Decision node are available with improvements over prior versions.
release
- Adds v2.0 of the LDAP Decision node and the Identity Store Decision node with improvements over prior versions. changelog · Oct 2026 · source · release history
- Adds v2.0 of the LDAP Decision node and the Identity Store Decision node with improved username handling. 14 Sep 2026 (2026-09-15) · Sep 2026 · source · release history
reCAPTCHA Enterprise node misconfiguration logging shipped The reCAPTCHA Enterprise node logs errors when its Google project, site key, or API key secret is misconfigured.
release
- Adds logging of errors in the reCAPTCHA Enterprise node when its Google project, site key, or API key secret is misconfigured. changelog · Oct 2026 · source · release history
- Adds error logging to the reCAPTCHA Enterprise node when its Google project, site key, or API key secret is misconfigured. changelog · Sep 2026 · source · release history
Authorize gateway shutdown on policy retrieval failure documented An Authorize gateway instance logs an error and shuts down if it cannot retrieve the latest authorization policy version from PingOne or from locally stored deployment configuration.
docs
-
September 28 Authorize gateway 1.2.2 Gateway instance shutdown behavior If a gateway instance can’t retrieve the latest authorization policy version from PingOne or the locally stored deployment configuration, it now logs an error message and shuts down.
docs update · Sep 2026
· source
- September 28 Authorize gateway 1.2.2 Gateway instance shutdown behavior If a gateway instance can’t retrieve the latest authorization policy version from PingOne or the locally stored deployment configuration, it now logs an error message and shuts down. docs update · Sep 2026 · source
Backchannel transaction redirect URI customization and subject recording shipped Administrators can customize backchannel transaction redirect URIs, and the system records the authenticated subject upon transaction completion even without an active session.
release
-
Enables customization of backchannel transaction redirect URIs via
redirectUrlTypeandcustomRedirectUrlparameters 14 Sep 2026 (2026-09-15) · Sep 2026 · source · release history - Records authenticated subject on backchannel transaction completion even without a session 14 Sep 2026 (2026-09-15) · Sep 2026 · source · release history
IGA certificate template management shipped Administrators can delete certificate templates directly from the IGA user interface.
release
- Adds the ability to delete certificate templates via the IGA UI. changelog · Sep 2026 · source · release history
- IGA now lets you delete certificate templates via the UI. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
IGA post-launch campaign editing shipped Administrators can modify the title and owner of an IGA campaign after it has been launched.
release
- Adds the ability to change campaign title and owner after a campaign has been launched. changelog · Sep 2026 · source · release history
- IGA now lets you change the campaign title and owner after a campaign is launched. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
IGA correlation rules for unmanaged applications shipped Administrators can configure IGA correlation rules to link aggregated accounts to identities during account aggregation for unmanaged applications.
release
- IGA correlation rules for unmanaged applications let administrators link aggregated accounts to identities during account aggregation. 02 Sep 2026 (2026-09-03) · Sep 2026 · source · release history
- config: IGA correlation rules for unmanaged applications allow linking aggregated accounts to identities during account aggregation 02 Sep 2026 · Sep 2026 · source · release history
PingOne-to-PingOne provisioning connection documented Users and groups can be provisioned between two PingOne environments within the same organisation.
docs
-
August 6 PingOne provisioning connection You can now provision users and groups between two PingOne environments within the same organization. Learn more in Provisioning the PingOne connection with a PingOne environment Verify configuration in PingOne Verify policies
docs update · Aug 2026
· source
-
August 6 PingOne provisioning connection You can now provision users and groups between two PingOne environments within the same organization. Learn more in Provisioning the PingOne connection with a PingOne environment Verify configuration in PingOne Verify policies
docs update · Aug 2026
· source
hCaptcha localization on hosted journey pages shipped CAPTCHA challenges shown to users on hosted journey pages are displayed in the user's own configured language.
release
- Hosted journey pages now display hCaptcha text and challenges in the end user's configured locale. changelog · Jul 2026 · source · release history
- Localizes hCaptcha text and challenges on hosted journey pages to match the end user's configured locale. 08 Jul 2026 (2026-07-09) · Jul 2026 · source · release history
Persistent column visibility preferences in data tables shipped Users can customise which columns are visible in data tables, and those preferences are remembered across sessions.
Also counts toward: Web management console
release
- Column visibility preferences for data tables in the admin console and hosted account pages are now customizable and saved between sessions. changelog · Jul 2026 · source · release history
- Makes column visibility preferences for data tables in the admin console and hosted account pages customizable and persistent across sessions. 08 Jul 2026 (2026-07-09) · Jul 2026 · source · release history
LDAP group filters for inbound provisioning documented Administrators can control which LDAP groups are synchronised into PingOne by applying configurable filter criteria on the LDAP gateway.
docs
-
We’ve released LDAP gateway client application version 4.4.0. This version supports group LDAP filters for inbound provisioning, enabling you to sync LDAP groups selectively into PingOne based on configurable filter criteria. Learn more in LDAP gateways
docs update · Jul 2026
· source
-
We’ve released LDAP gateway client application version 4.4.0. This version supports group LDAP filters for inbound provisioning, enabling you to sync LDAP groups selectively into PingOne based on configurable filter criteria. Learn more in LDAP gateways
docs update · Jul 2026
· source
App Policy Decision node for journey access control shipped An App Policy Decision node is available to enforce OIDC and SAML application access policies in journeys with filtering by group or organization.
release
- New App Policy Decision node enables enforcing OIDC and SAML application access policies in journeys with filtering by group, organization, etc. 24 Mar 2026 · Mar 2026 · source · release history
- Policy Decision node evaluates authorization policies against resources within an authentication journey 18 Mar 2026 · Mar 2026 · source · release history
Hosted account device management shipped Users can view last sign-on times, add dates, edit device names, and delete devices directly from hosted account pages.
release
- Adds new device management capabilities in hosted account pages, allowing users to view last sign-on time, add date, edit device name, and delete devices 18 Feb 2026 · Feb 2026 · source · release history
example
-
Users can now manage their registered devices directly from the hosted account interface, including renaming or removing them.
In the hosted account pages, navigate to the Devices section for each device to view metadata and manage it.18 Feb 2026 · Feb 2026 · source
PingOne Protect Evaluation custom identifiers shipped The PingOne Protect Evaluation node supports configuration properties to specify a custom session ID, browser cookie, and external deviceId.
release
-
PingOne Protect Evaluation node adds configuration properties to specify a custom session ID, custom browser cookie, and external
deviceId13 Feb 2026 · Feb 2026 · source · release history
example
-
Include a custom device ID and browser cookie in PingOne Protect evaluations via configuration properties
curl -X PUT 'https://<aic-host>/idp/rest/realm-config/services/pingIdentityPingOneProtectEvaluation' -H 'Content-Type: application/json' -d '{"customDeviceId": "<device-id>", "customBrowserCookie":…13 Feb 2026 · Feb 2026 · source
PingOne Worker connectivity testing shipped A testConnection action is available on the PingOne Worker service endpoint to verify connectivity from Advanced Identity Cloud to PingOne.
Also counts toward: REST API
release
-
New
testConnectionaction on/realm-config/services/pingOneWorkerService/workers/<pingone-worker-service-name>endpoint tests connectivity from Advanced Identity Cloud to PingOne 13 Feb 2026 · Feb 2026 · source · release history
example
-
Verify connectivity from Advanced Identity Cloud to PingOne using the new REST action
curl -X POST 'https://<aic-host>/idp/rest/realm-config/services/pingOneWorkerService/workers/<pingone-worker-service-name>?action=testConnection' -H 'Authorization: Bearer <token>'13 Feb 2026 · Feb 2026 · source
RADIUS and consent authentication flows shipped RADIUS Decision nodes can capture vendor-specific attributes, and pushed consent requests support remote agent credentials for secure authentication.
release
- RADIUS Decision node captures Vendor-Specific Attributes (VSA) returned by the RADIUS server during authentication 13 Feb 2026 · Feb 2026 · source · release history
- Pushed consent requests can now include remote consent agent credentials in a Basic Authentication header 13 Feb 2026 · Feb 2026 · source · release history
AIC Remote MCP Server for AI agent administration shipped An opt-in, centrally hosted HTTP-based Model Context Protocol server lets AI agents and development assistants administer Advanced Identity Cloud via natural-language prompts over OAuth 2.0 authentication.
Also counts toward: MCP server, Natural-language query
release
- Ping Identity adds the AIC Remote MCP Server, an opt-in, centrally hosted HTTP-based Model Context Protocol server that lets AI agents and development assistants administer Advanced Identity Cloud via natural-language prompts over OAuth 2.0 authentication — available now in sandbox… changelog · Oct 2026 · source · release history
Delegated administrator relationship property visibility in hosted account pages shipped Delegated administrators can view their own relationship properties directly in the hosted account pages.
release
- Delegated administrators can now view their own relationship properties in the hosted account pages. changelog · Oct 2026 · source · release history
IGA workflow definition size limit increase shipped Identity Governance accepts workflow definitions up to 1 MiB, raising the previous size limit.
release
- Identity Governance now accepts workflow definitions up to 1 MiB. changelog · Oct 2026 · source · release history
QR code generation in scripted journey nodes shipped Scripted nodes can generate QR codes via a callbacksBuilder.qrCodeCallback() binding, rendering them in hosted pages or apps built with the Ping SDKs.
release
- Ping Identity adds a callbacksBuilder.qrCodeCallback() binding for scripted nodes, letting them generate QR codes that render in hosted pages or apps built with the Ping SDKs. changelog · Oct 2026 · source · release history
Unique username and application name enforcement shipped The underlying datastore enforces uniqueness for usernames and application names at the storage level.
release
- The underlying datastore now enforces unique usernames and application names. changelog · Oct 2026 · source · release history
Certificate Collector and Certificate Validation node v2.0 shipped Version 2 of the Certificate Collector and Certificate Validation nodes is available with security hardening improvements.
release
- Version 2 of the Certificate Collector and Certificate Validation nodes includes security hardening improvements. 22 Oct 2026 (2026-10-23) · Oct 2026 · source · release history
EC key attestation for Android device binding shipped EC key attestation is supported for Android device binding, enabling compatibility with newer Google hardware attestation root certificates.
release
- Adds EC key attestation support for Android device binding, enabling compatibility with newer Google hardware attestation root certificates. changelog · Oct 2026 · source · release history
Multi-node selection in journey designer shipped Multiple journey nodes can be selected at once by holding Shift and clicking each node.
release
- Enables selecting multiple journey nodes by holding Shift and clicking each node. 28 Sep 2026 (2026-09-29) · Sep 2026 · source · release history
OAuth 2.0 audience token introspection shipped The OAuth 2.0 provider includes a setting that allows audience members to introspect tokens.
release
- Adds Allow audience members to introspect tokens setting on the OAuth 2.0 provider 14 Sep 2026 (2026-09-15) · Sep 2026 · source · release history
Hosted IdP authentication request storage configuration shipped The hosted IdP provides an option to configure the storage location for SAML authentication requests.
release
- Hosted IdP adds Authentication Request Storage option to configure SAML authentication request storage location. 14 Sep 2026 · Sep 2026 · source · release history
HubSpot provisioning connection documented Users and groups can be provisioned between a HubSpot account and PingOne, keeping the two systems in sync.
docs
-
DaVinci audit events released for general availability We’ve released DaVinci administrative audit events for general availability. You can find them listed in DaVinci administrative audit events July 30 HubSpot provisioning connection You can now provision users and groups between your HubSpot account and PingOne.
docs update · Jul 2026
· source
Page node v3 with per-validation CAPTCHA token generation shipped When CAPTCHA and live password validation are used together in a journey, a fresh CAPTCHA token is generated for each validation attempt to prevent failures.
release
- Page node v3 is now available, generating a new CAPTCHA token for each validation request when both CAPTCHA and live password validation are used together. changelog · Jul 2026 · source · release history
Managed secrets in custom scripted nodes shipped Custom scripted nodes can pull sensitive values from a managed secret store rather than embedding them in script code.
release
-
Custom scripted nodes can now reference managed secrets from a secret store using a
SECRETproperty type, keeping API keys and passwords out of script code. 21 Jul 2026 (2026-07-22) · Jul 2026 · source · release history
MFA secret key length default increase shipped The default minimum secret key length for OATH and Combined MFA Registration nodes has increased to 40 characters.
release
- The default Minimum Secret Key Length on the OATH Registration and Combined MFA Registration nodes has increased from 32 to 40 characters 21 Jul 2026 · Jul 2026 · source · release history
Account status visibility on Identities page shipped Administrators can see at a glance whether each user account is active or inactive from the Identities page.
release
- Adds an Account Status column (Active/Inactive) to the Identities page. 08 Jul 2026 (2026-07-09) · Jul 2026 · source · release history
OAuth 2.0 mutual TLS authentication shipped Administrators can configure trusted CA certificates directly on OAuth 2.0 clients to enforce mutual TLS authentication.
release
- You can now configure a trusted CA certificate for each OAuth 2.0 client using the tls_client_auth authentication method via OPENAM-27540. 04 Jun 2026 (2026-06-05) · Jun 2026 · source · release history
SaaS provisioning filter policies shipped Filter policies can be added to object types for SaaS REST applications to reduce network overhead during provisioning.
release
- SaaS REST and SaaS REST (connector server) applications now let you add filter policies to object types when configuring provisioning to reduce network overhead. 04 Jun 2026 (2026-06-05) · Jun 2026 · source · release history
OIDC SP adapter AuthnRequest helper shipped Next-generation SP adapter scripts can use the authnRequestHelper binding to retrieve and modify the destination property of the AuthnRequest.
release
-
Adds
authnRequestHelperbinding for next-generation SP adapter scripts to retrieve and modify the destination property of the AuthnRequest 17 Apr 2026 · Apr 2026 · source · release history
Identity governance access modeling shipped Identity governance provides machine learning-driven role mining capabilities to discover potential access roles based on historical usage patterns.
Also counts toward: ML-based detection
release
- Added Access Modeling (role mining) feature in Identity Governance to discover potential access roles using machine learning. 14 Apr 2026 · Apr 2026 · source · release history
Journey session timeout configuration in admin console shipped Journey editors in the admin console can now override authenticated session timeout, maximum session time, and maximum idle time via UI options.
Also counts toward: Web management console
release
- Added UI options Override authenticated session timeout, Maximum Session Time, and Maximum Idle Time in the admin console journey editor (previously REST-only). 14 Apr 2026 · Apr 2026 · source · release history
OAuth 2.0 Token Exchange audience control shipped Token Exchange requests can now specify allowlisted audience parameters that are included in the resulting token's aud claim.
release
-
OAuth 2.0 Token Exchange now supports specifying audience parameters that are allowlisted and included in the resulting token's
audclaim 24 Mar 2026 · Mar 2026 · source · release history
SAML error page HTTP binding override shipped An environment variable allows overriding the HTTP binding (HTTP-POST or HTTP-Redirect) used for SAML error page redirects.
release
-
Adds the
esv-global-saml-error-page-http-bindingenvironment variable to override the HTTP binding (HTTP-POST or HTTP-Redirect) used for SAML error page redirects 18 Feb 2026 · Feb 2026 · source · release history
Journey localization binding shipped A new locales binding returns localized strings from a translation map in Journey Decision, Configuration Provider, and Device Match node scripts.
release
-
New
localesbinding returns localized strings from a translation map in Configuration Provider, Journey Decision, and Device Match node scripts 13 Feb 2026 · Feb 2026 · source · release history
SAML adapter scripting engine support shipped SAML 2.0 SP adapter, IDP adapter, and IDP attribute mapper scripts can now use the next-generation scripting engine with utils and openidm bindings.
Also counts toward: JavaScript scripting support, Scripting API, Scripting language support
release
-
SAML 2.0 SP adapter, IDP adapter, and IDP attribute mapper scripts can now use the next-generation scripting engine with
utilsandopenidmbindings 13 Feb 2026 · Feb 2026 · source · release history
SAML application context binding availability shipped Application context configuration is added to hosted IdP or remote SP entity config to make the samlApplication binding available for all SAML flows.
release
-
Adds
application contextconfiguration to hosted IdP or remote SP entity config to makesamlApplicationbinding available for all SAML flows 13 Feb 2026 · Feb 2026 · source · release history
PingOne Forms JSON content in dynamic text documented PingOne Forms renders JSON-formatted values as plain text in dynamic text fields on end-user forms.
docs
-
New features and improvements in PingOne DaVinci. Updated October 16, 2026. October 16 PingOne Forms now supports JSON contents in dynamic text Previously in PingOne Forms, including a JSON-formatted value in dynamic text had unexpected results. Now, JSON contents will render as text on the end user form.
seen Oct 2026
· source
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
7 commands for Ping Identity, each with where it came from. This tool has no source analysis yet, so there is no option reference and no captured run beside them.
No command matches.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for Ping Identity, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Ping Identity puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Website history
pingidentity.com, every changePing Identity's home page and 35 more pages as they looked each month from September 2021 to October 2026: 47 renders, 4 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Coverage
Missing something? Tell us
What Ping Identity connects to, runs on and detects, read from its release notes and docs. So far: 3 new integrations, 1 new supported platform, 1 updated integration.
5 changes, tracked since Oct 5, 2026.
-
Oct 62026
new YubiKey support in MFA Use Case Connector
YubiKey support: YubiKey devices have their own device type for registration and dedicated outcome paths for authentication.
-
Oct 62026
new PingID Desktop support in MFA Use Case Connector
PingID Desktop support: PingID Desktop appears as a device type for registration and as a passwordless authentication option with its own output paths and outcomes.
-
Oct 52026
new Microsoft Entra ID email provider integration
IAM-10741: The Advanced Identity Cloud admin console now lets you configure Microsoft Entra ID or custom SMTP email providers and send test emails.
-
Oct 52026
new EC key attestation for Android device binding
With Google hardware attestation root certificates
OPENAM-26135: EC key attestation is now supported for Android device binding, resolving key attestation failures with newer Google hardware attestation root certificates.
-
Oct 52026
updated LexisNexis DDP node renaming and IIDQA shared state update
With LexisNexis Dynamic Decision Platform (DDP), LexisNexis InstantID Question and Answer (IIDQA)
OPENAM-28247 TNTP-278: The ThreatMetrix nodes have been renamed to LexisNexis Dynamic Decision Platform (DDP) nodes. The LexisNexis InstantID Question and Answer (IIDQA) nodes have been updated to store the decision API responses in shared state.
Identity & access 3
Other 2
Identity & access 1
Operating systems 1
Nothing first seen in this window. That doesn't mean Ping Identity shipped nothing, only that we found no record of it.
How we count
Read from 13 of 96 release notes and docs updates we hold for Ping Identity. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through Ping Identity's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
96 entries
No entries match these filters.
- October 202617
- September 202634
- August 202617
- July 202617
- June 20262
- April 20263
- March 20263
- February 20263
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →