Cloudsmith
changelog-20261028-eab54908 commercialThe section your link pointed to isn't on Cloudsmith's page any more, so we've brought you to the top.
Cloudsmith is a fully-managed artifact management, software supply chainsoftware supply chainThe dependencies, tools and processes used to build and deliver software. Compromising one part can affect the products or organizations that rely on it. security, and software distribution platform.
cloudsmith update
cloudsmith --workspace <workspace-slug> <subcommand>
credential-helper pnpm --workspace WORKSPACE
credential-helper uninstall pnpm --dry-run
cloudsmith push myorg/mynixrepo abc123def456.nar --narinfo-file abc123def456.narinfo --tags nix,ci
extra-substituters = https://token:TOKEN@nix.cloudsmith.io/myorg/mynixrepo
cloudsmith upstream create myorg/mynixrepo nix-upstream.json
# 1. Add the registry (no token) in ~/.cargo/config.toml
# [registries]
# my-org-myrepo = { index = "sparse+https://cargo.cloudsmith.io/my-org/my-repo/" }

# 2. Install the credential helper, discovering custom domains for the workspace
credential-helper --workspace my-org
[registries]
my-org-my-repo = { index = "sparse+https://cargo.cloudsmith.io/my-org/my-repo/" }

[registry]
global-credential-providers = ["cargo:token", "cargo-credential-cloudsmith"]
credential-helper list
credential-helper uninstall
STORE_PATH="$(readlink -f result)"
nix copy --to 'https://nix.cloudsmith.io/OWNER/REPOSITORY' --no-check-sigs "$STORE_PATH"
extra-substituters = https://nix.cloudsmith.io/OWNER/REPOSITORY
extra-trusted-public-keys = KEY_NAME:PUBLIC_KEY
extra-substituters = https://nix.cloudsmith.io/OWNER/REPOSITORY https://cache.nixos.org
extra-trusted-public-keys = KEY_NAME:PUBLIC_KEY cache.nixos.org-1:6NCHdD59X431o0gWypbMrAURkbJ16ZPMQFGspcDShjY=
resource "cloudsmith_connected_repository" "example" {
  # configuration fields here
}
Summary
Cloudsmith is a commercial artifact management and software supply chain security platform, run as a fully-managed SaaSSaaSSoftware delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally. service rather than something you self-host. It stores and distributes packages across formats while layering in policy-as-code enforcement, continuous vulnerability and malicious-package detection sourced from OSV.devOSV.devAn open-source vulnerability database and API maintained by Google that aggregates CVEs and ecosystem-specific advisories in a unified schema, giving cyber tools a single feed to query for package-level vulnerability data., and cooldown periods that quarantine newly published NuGetNuGetMicrosoft's package manager for .NET, hosting a public registry of reusable libraries so tools can pull in dependencies without bundling or manually maintaining third-party code., Go, and Maven packages before they can be consumed. It's aimed at platform engineers and application teams managing package registries and CI/CD pipelines, with OIDCOIDCOpenID Connect, a sign-in protocol built on OAuth 2.0. An application uses identity information from a trusted provider instead of maintaining a separate password for each user.-based authentication and a standalone CLI replacing static API keys and manual Docker logins. Its documentation doesn't name a direct competitor, but it sits in the same space as artifact repository and software supply chain security tools. Launched in 2016 and still active, with 25 tracked releases and the most recent just 22 days ago.
Cloudsmith is a fully-managed artifact management, software supply chain security, and software distribution platform.
How Cloudsmith helps
Which of my newly published packages could still be pulled into a build before anyone's had a chance to review them?
quarantines new NuGet, Go, and Maven versions for a configured delay period after publish, so nothing consumable is a fresh, unvetted upload
Which packages in my workspace have a known vulnerability or look malicious right now?
checks every package continuously against OSV.dev advisories, including ecosystem-native version ranges for Debian, Alpine, and PyPI, without waiting for a scheduled or manual scan
Where did this artifact actually come from and what CI run produced it?
lets you attach structured key-value metadata to a package, so build info, git provenance, and compliance evidence travel with the artifact itself
Can my pipelines authenticate without a static key sitting in a secrets store?
discovers OIDC credentials from the CI/CD platform automatically and, for container registries, hands off login to a credential helper instead of a stored password
Would this proposed policy change actually break anything before I roll it out?
the policy editor flags Rego syntax and logic errors inline as you write, and policies can be versioned and applied through Terraform so a change goes through the same review as any other infrastructure code
Am I hitting registry rate limits because I'm pulling anonymously?
Docker Hub and hardened-image upstreams can run through Cloudsmith-managed authentication, which qualifies for higher pull rate limits than anonymous access
Languages
Features
Built from Cloudsmith's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- Cloudsmith covers 1 of the 2 secrets and credential hygiene capabilities we track.
- Cloudsmith covers 1 of the 2 vulnerability management capabilities we track.
What Cloudsmith offers you
- Command-line interface9
- Web management console3
- CI/CD pipeline integration2
- REST API2
- Terraform provider2
- CSV data export1
- JSON data export1
- Role-based access control1
No capabilities match.
OIDC SSO 1 feature Identity and access since 2026
OIDC-based CI/CD authentication shipped Lets CI/CD pipelines authenticate to Cloudsmith using short-lived OIDC tokens issued by the platform rather than stored API keys.
Shared capability: OIDC SSO
Also counts toward: CI/CD pipeline integration
release
- Adds OIDC authentication for Buildkite pipelines and Google Cloud workloads in CLI v1.29.0, eliminating the need to store Cloudsmith API keys on build hosts. changelog · Oct 2026 · source · release history
- Adds OIDC authentication support for Google Cloud workloads, eliminating the need to store Cloudsmith API keys on build hosts. CLI v1.29.0: OIDC for Buildkite and Google Cloud, and listing packages from connected repositories (2026-10-15) · Oct 2026 · source · release history
- Adds OIDC authentication support for Buildkite pipelines, eliminating the need to store Cloudsmith API keys on build hosts.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ CLI v1.29.0: OIDC for Buildkite and Google Cloud, and listing packages from connected repositories (2026-10-15) · Oct 2026 · source · release history
- Automatically discovers OpenID Connect (OIDC) credentials for all major CI/CD platforms, eliminating the need for static API keys in pipelines. CLI v1.19.0: Authenticate automatically with OIDC and Docker credential discovery (2026-07-23) · Jul 2026 · source · release history
Secret scanning 1 feature Secrets and credential hygiene since 2026
GitHub secret scanning integration shipped Works with GitHub's secret scanning programme to detect and alert on Cloudsmith API keys that have been accidentally committed to repositories.
Shared capability: Secret scanning
release
- GitHub secret-scanning email notifications now list every location an exposed Cloudsmith API key was found in a GitHub repository, with a direct link to each detection. changelog · Sep 2026 · source · release history
-
The Cloudsmith workspace audit log records an
API_KEY_EXPOSEDevent for each detection, including the masked key and specific detection location. GitHub secret scanning notifications now link to each detection location · Sep 2026 · source · release history - GitHub secret scanning email notifications now list every detection location for an exposed Cloudsmith API key, with a direct link to each occurrence in the GitHub repository.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub secret scanning notifications now link to each detection location (2026-09-11) · Sep 2026 · source · release history
- Email notifications for exposed Cloudsmith API keys in GitHub repositories list every detection with a direct link to the specific location. GitHub secret scanning notifications now link to each detection location · Sep 2026 · source · release history
- Integrates with GitHub secret scanning partner program to automatically detect exposed Cloudsmith API keys in repositories. Cloudsmith API keys are now detectable by GitHub secret scanning (2026-07-03) · Jul 2026 · source · release history
example
-
Enable GitHub secret scanning on your repository so exposed Cloudsmith API keys are flagged automatically before they can be exploited.
In the GitHub repository, go to Settings > Security > Code security and analysis, then enable Secret scanning.Cloudsmith API keys are now detectable by GitHub secret scanning (2026-07-03) · Jul 2026 · source
Vulnerability scanning 1 feature Vulnerability management since 2026
Vulnerability scanning shipped Automatically scans every stored package for known vulnerabilities and malicious content using OSV.dev advisories, continuously and without manual intervention.
Shared capability: Vulnerability scanning
release 7 total
-
Adds Download vulnerability data option on the package Overview tab to export matched vulnerability and malicious package records as a JSON file
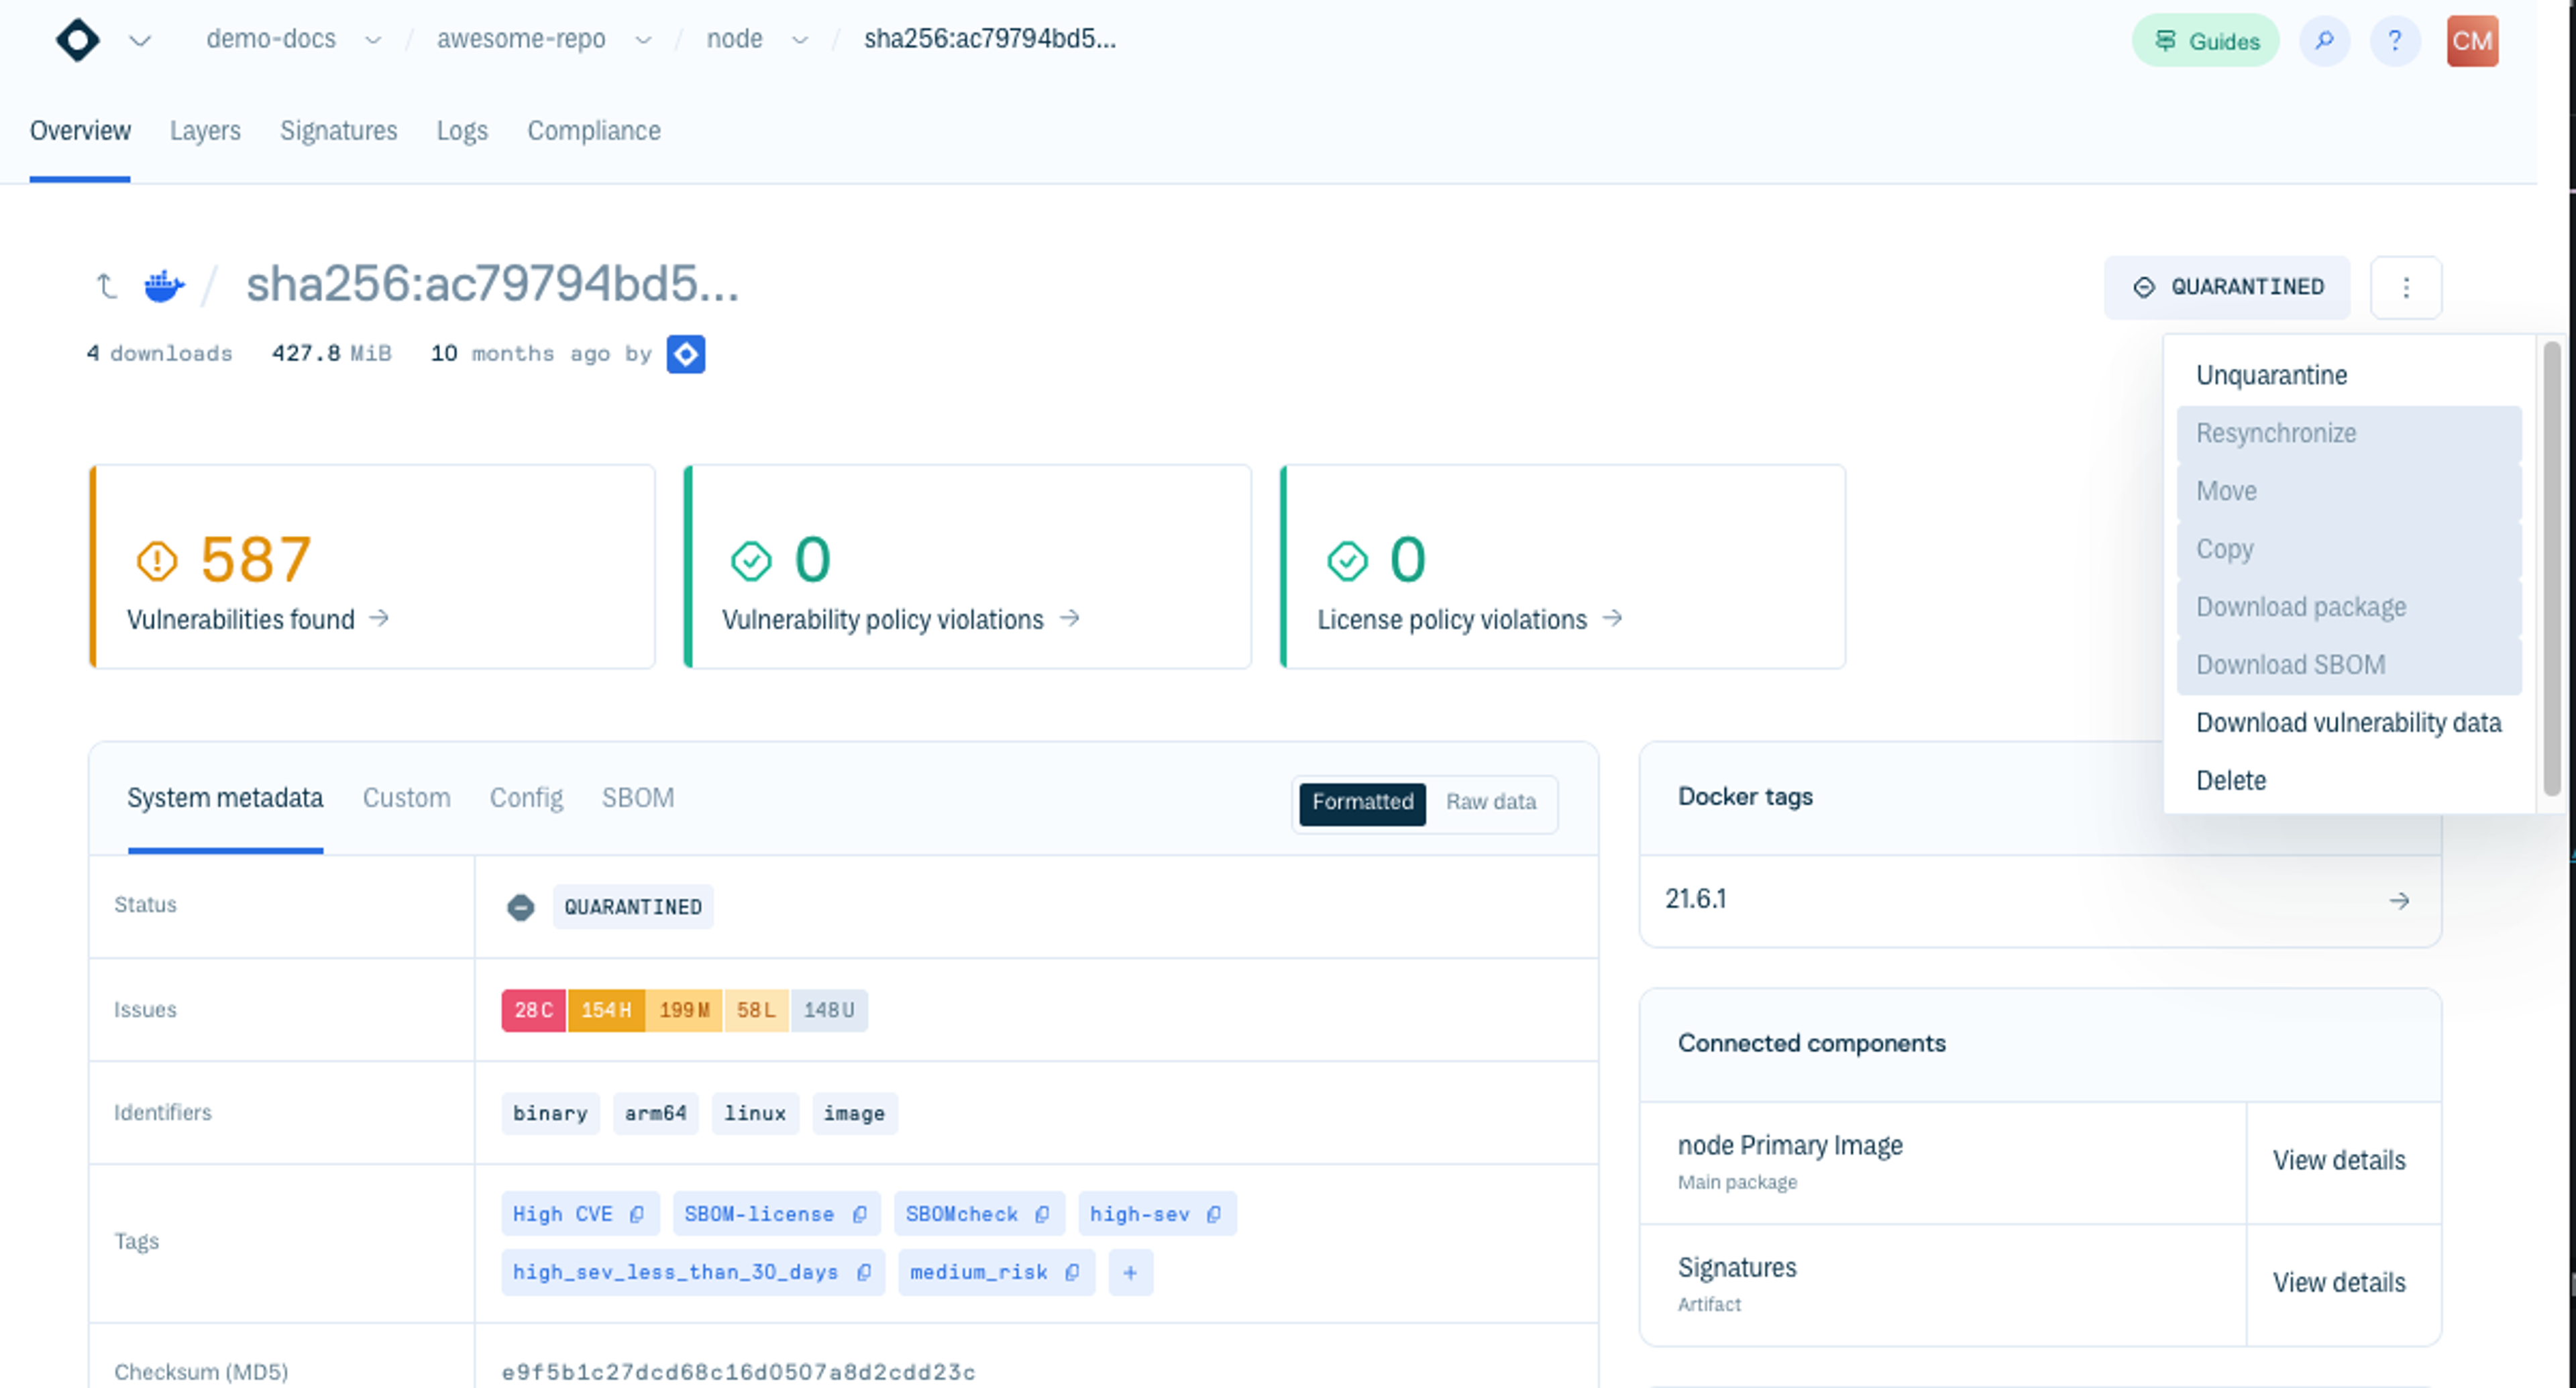 Download package vulnerability findings from the Cloudsmith web app · Sep 2026
· source
· release history
- OSV.dev now replaces Trivy as the vulnerability data source shown in the web app and API for risk detection. changelog · Aug 2026 · source · release history
- Continuous risk detection is now generally available, automatically checking every package in a workspace against known vulnerabilities and malicious packages with no scheduled or manual rescans required. changelog · Aug 2026 · source · release history
- Every package in your workspace is now checked automatically against known vulnerabilities and malicious packages, with no scheduled or manual rescans required. Continuous risk detection is now generally available (2026-08-12) · Aug 2026 · source · release history
- Replaces Trivy with OSV.dev as the data source powering vulnerability results in the web app and API, unifying it with the source that has driven policy evaluation since early access. Continuous risk detection is now generally available (2026-08-12) · Aug 2026 · source · release history
- Enables continuous, automatic vulnerability and malicious-package checking for every package in a workspace — no scheduled or manual rescans required. Continuous risk detection is now generally available (2026-08-12) · Aug 2026 · source · release history
example
-
Review and archive all vulnerability findings for a package outside the UI — useful for feeding results into a SIEM or ticketing system.
In the Cloudsmith web app, open the repository, navigate to the target package, go to the Security or Vulnerabilities tab, and click 'Export' to download findings as a JSON file.changelog · Sep 2026 · source -
Download a snapshot of all vulnerability and malicious package findings for offline analysis or compliance reporting.
In the Cloudsmith web app, navigate to your repository's vulnerability findings view and select the option to export findings as a JSON file.Download package vulnerability findings from the Cloudsmith web app (2026-09-14) · Sep 2026 · source
Other / not yet classified 33 features Features we have not matched to a capability yet. A suggested match is marked.
CLI standalone binary shipped Provides the Cloudsmith CLI as a self-contained binary that runs on Linux, macOS, and Windows without requiring a local Python environment.
Also counts toward: Command-line interface
release 14 total
-
CLI v1.21.0–v1.26.0 adds
pushsupport for Nix packages. changelog · Oct 2026 · source · release history - CLI v1.21.0–v1.26.0 adds commands to manage a repository's GPG key and access privileges from the terminal. changelog · Oct 2026 · source · release history
- Enables GPG key management for repositories directly from the CLI, without using the web UI. CLI v1.21.0 to v1.26.0: Nix support, Cargo and pnpm credential helpers, and repository administration from your terminal (2026-09-28) · Sep 2026 · source · release history
- Enables repository access-privilege administration from the CLI terminal. CLI v1.21.0 to v1.26.0: Nix support, Cargo and pnpm credential helpers, and repository administration from your terminal (2026-09-28) · Sep 2026 · source · release history
-
Adds a per-package audit trail in the Cloudsmith web app showing what changed, who changed it, and when.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
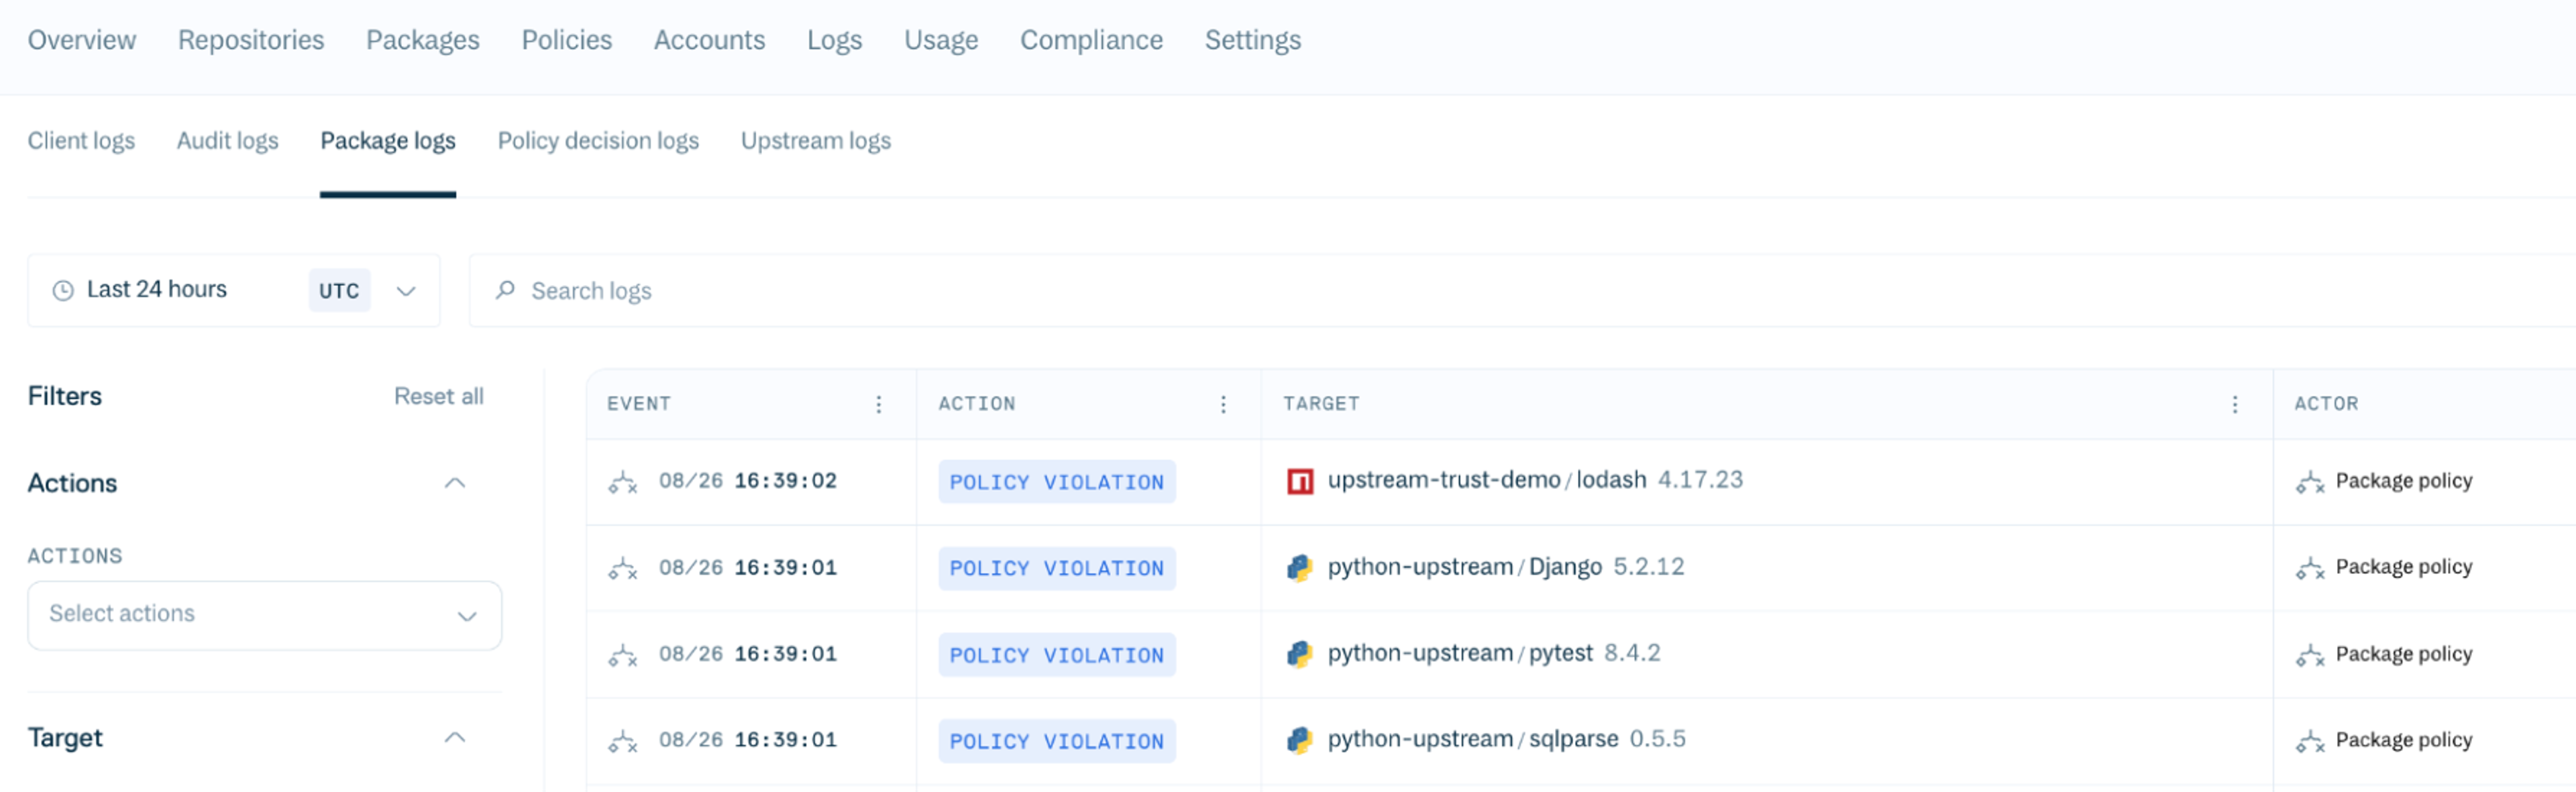 Track every change to your packages with package logs (2026-09-14) · Sep 2026
· source
· release history
- Enables filtering package logs by action (Copy, Delete, Hard delete, Move, Policy violation, Quarantine, Restore, Resync, Sync, Tags changed) to isolate specific events Track every change to your packages with package logs · Sep 2026 · source · release history
docs
- CLI 1.20.0 no longer requires Python The Cloudsmith CLI now ships as a standalone, self-contained binary for Linux, macOS, and Windows. This eliminates its dependency on a local Python environment. changelog · Aug 2026 · source
example
-
Install the new standalone CLI on any platform without managing a Python runtime.
curl -fsSL https://get.cloudsmith.com/cli/install.sh | shCLI 1.20.0 no longer requires Python (2026-07-30) · Jul 2026 · source
Policy management shipped Lets teams write, test, and automatically trigger supply-chain rules as Rego code that gates or controls packages across the workspace.
Also counts toward: Terraform provider, Web management console
release 11 total
-
Adds a
validateAPI endpoint that returns syntax and type errors in Rego policy logic without creating or updating anything, enabling pre-submission policy checks.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ changelog · Oct 2026 · source · release history - Extends cooldown policies to Conda and Docker packages, protecting supply chains from newly published versions that may carry malware or lack sufficient community scrutiny. changelog · Aug 2026 · source · release history
-
Adds
cooldownpolicy support for Conda and Docker package types Cooldown policies now support Conda and Docker (2026-08-27) · Aug 2026 · source · release history - Policy management is now generally available across the web app, API, and Terraform provider, enabling policy-as-code enforcement rules across the software supply chain. changelog · Aug 2026 · source · release history
- The policy editor now provides inline Rego error flagging and schema-field autocomplete as you type, surfacing mistakes before saving. changelog · Aug 2026 · source · release history
- Autocomplete in the policy editor now suggests schema fields as you type. Catch policy errors before you save (2026-08-12) · Aug 2026 · source · release history
docs
-
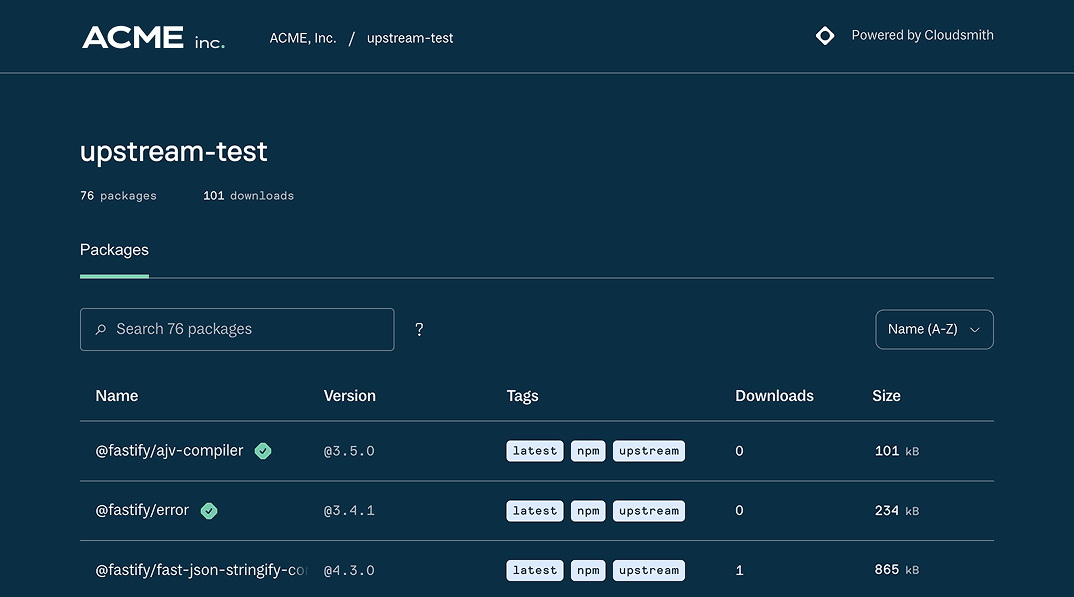
Broadcasts help you distribute your software packages to your end-users through a customizable, secure, and user-friendly interface. It allows you to create a seamless experience for your customers, making it feel as though they are interacting directly with your own infrastructure, rather than a third-party service.
 docs update · Aug 2026
· source
- About Cloudsmith Dependencies (for developers) Cloudsmith allows you to manage all your software assets within a single platform. With native support for 30 package formats, no matter what you are developing; Cloudsmith can help simplify and accelerate your development pipelines. seen Aug 2026 · source
- Announcement Policy management is now generally available Following early access, policy management - Cloudsmith's policy-as-code system for enforcing rules across your software supply chain - is now generally available across the web app, API, and Terraform provider… Aug 12 2026 Announcement Continuous risk detection… changelog · Aug 2026 · source
Upstream proxying and caching shipped Routes requests for external packages through Cloudsmith-managed proxies so teams get cached, rate-limited access to upstream registries without managing credentials themselves.
release 7 total
- Adds ActiveState Curated Catalog upstream support, configurable via the Libraries tab, so teams can proxy and cache packages from the ActiveState catalog.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ changelog · Oct 2026 · source · release history
-
Adds ActiveState Curated Catalog as a supported upstream source, with configuration available in the Libraries tab, enabling proxy and caching of curated packages.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
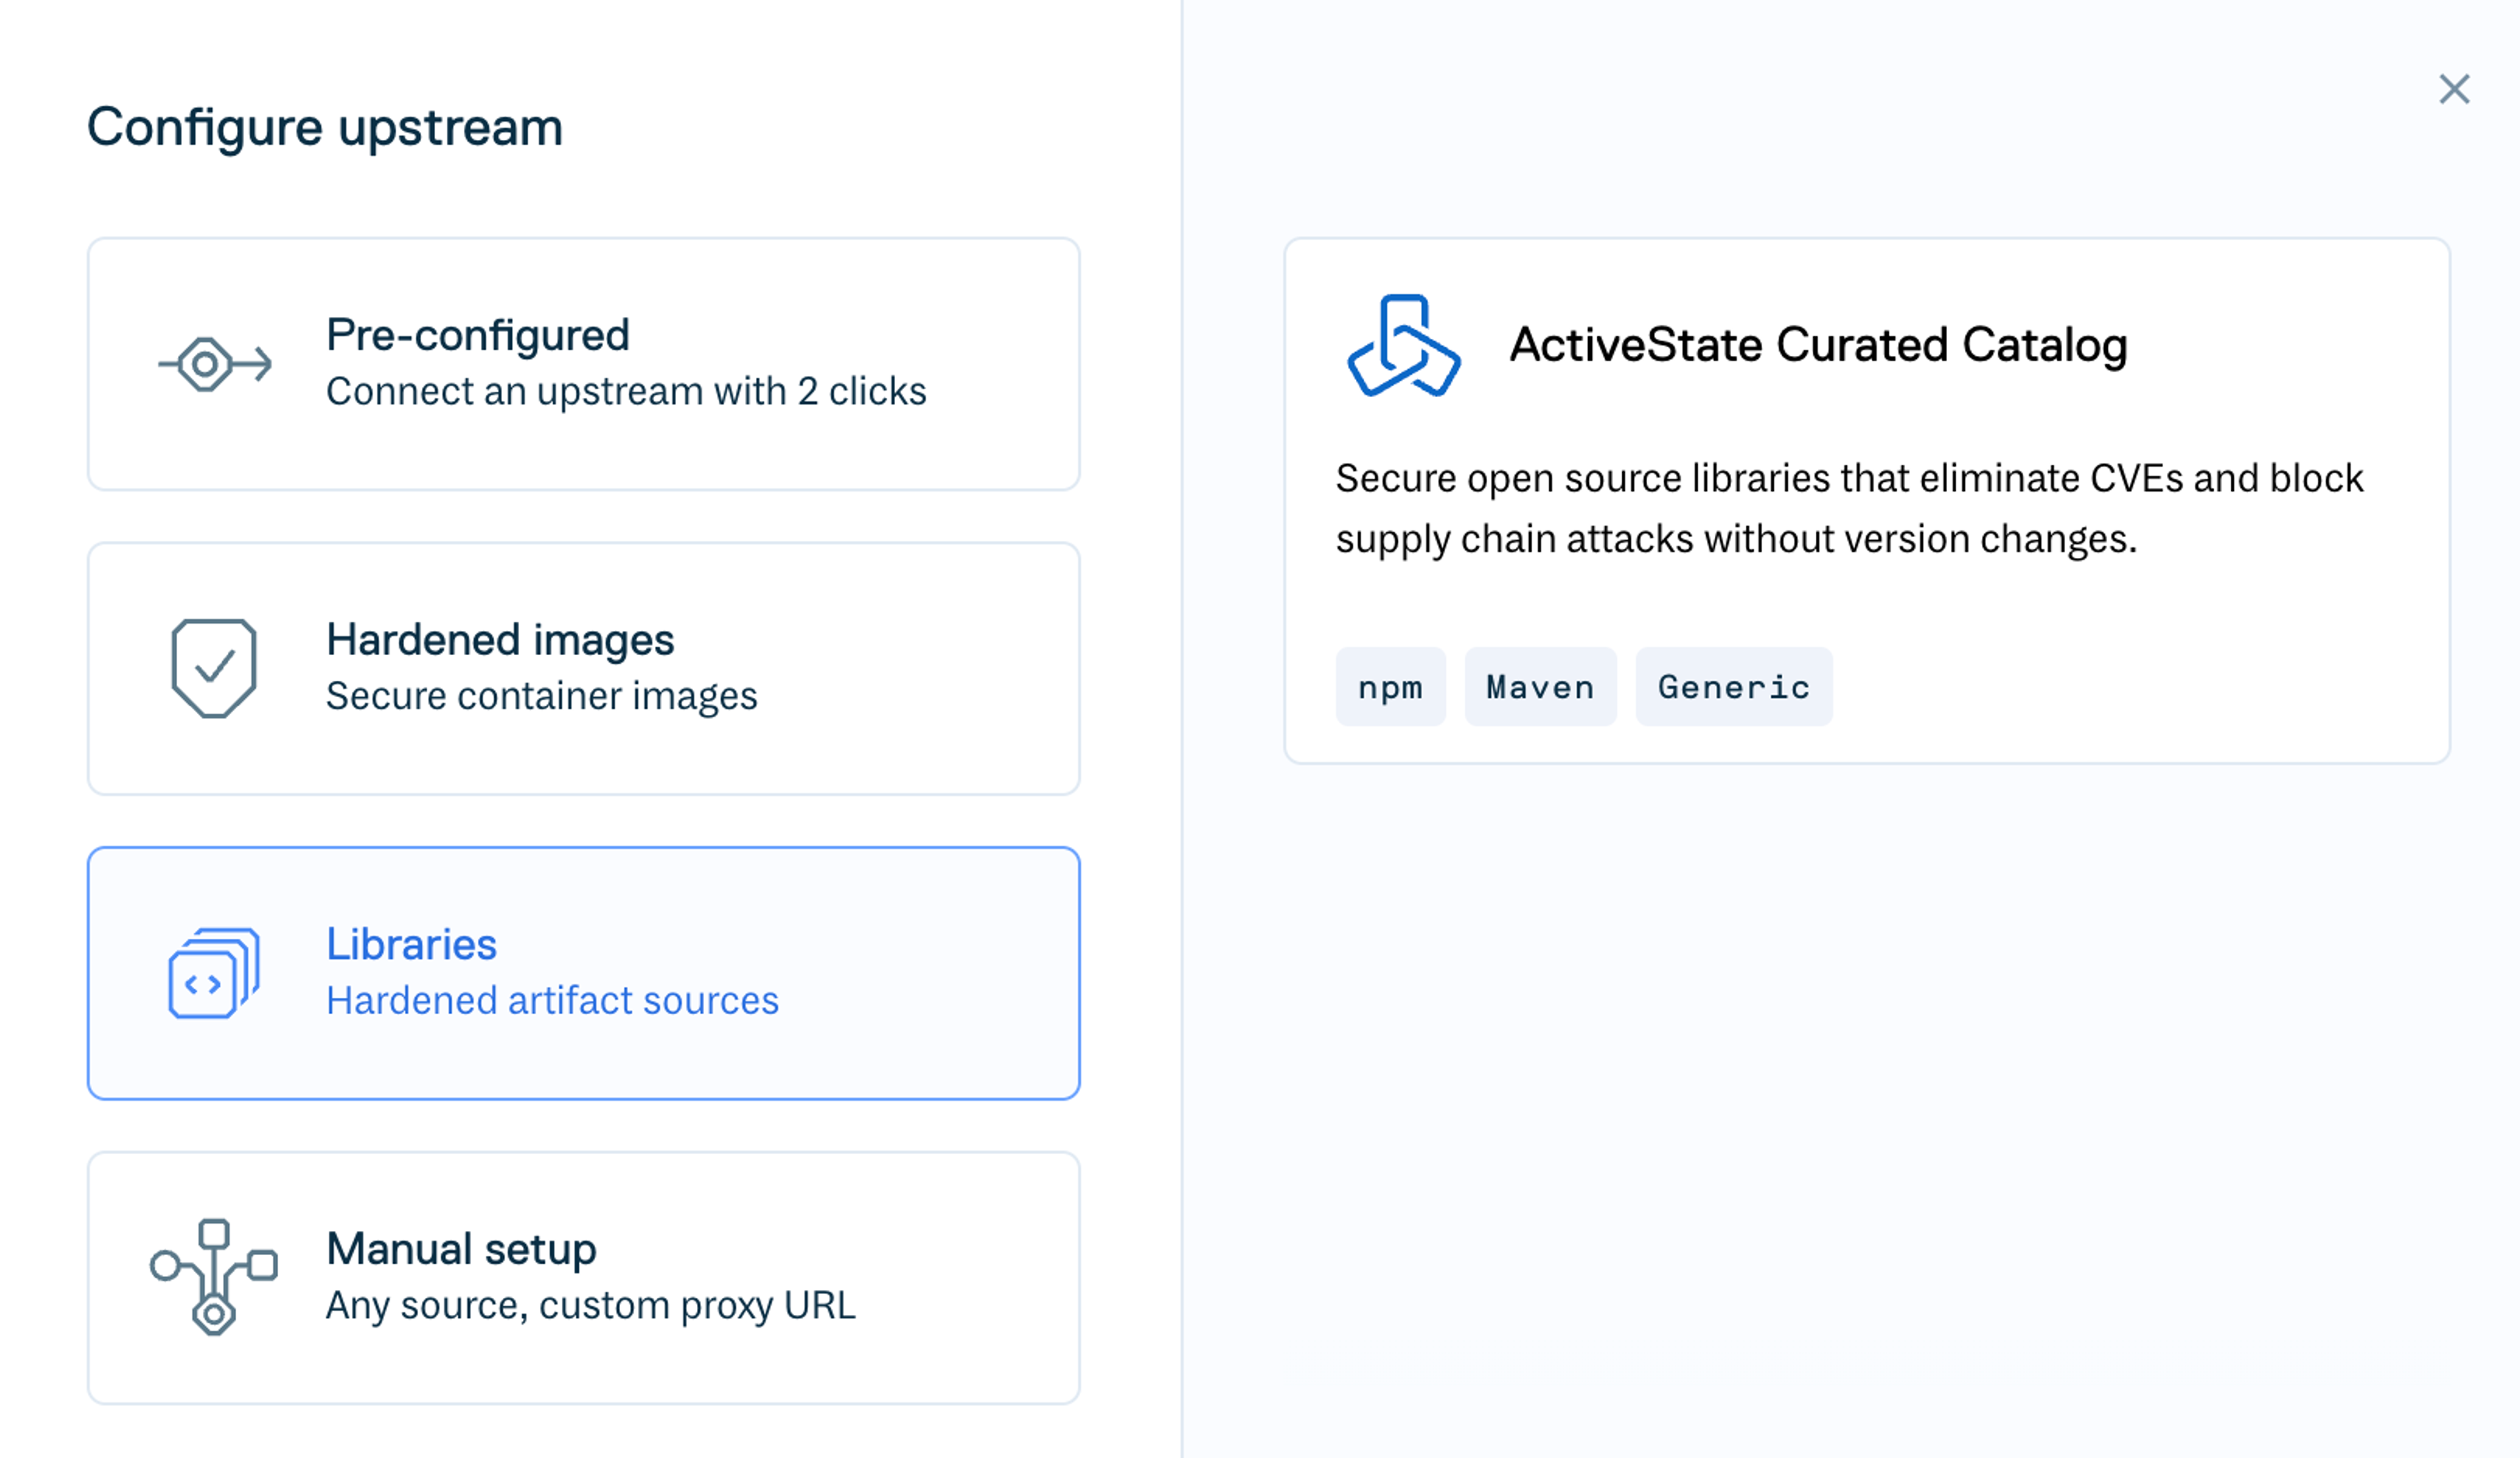 Proxy and cache packages from your ActiveState Curated Catalog (2026-10-15) · Oct 2026
· source
· release history
- Adds a Libraries tab for quickly configuring library registries as upstreams, providing access to vendor-curated, pre-vetted, and security-scanned open source package feeds. changelog · Aug 2026 · source · release history
- New Hardened Images tab enables proxying and caching hardened, minimal container images through upstreams without manual format or URL entry. Hardened images tab for configuring upstreams (2026-07-15) · Jul 2026 · source · release history
- Supports Cloudsmith-managed authentication for Docker Hub upstreams, eliminating the need to provide personal credentials. Set up Docker Hub and DHI upstreams with Cloudsmith-managed authentication (2026-06-29) · Jun 2026 · source · release history
- Enables higher Docker Hub and DHI pull rate limits automatically via managed authenticated tokens versus anonymous access. Set up Docker Hub and DHI upstreams with Cloudsmith-managed authentication (2026-06-29) · Jun 2026 · source · release history
example
-
Configure an ActiveState Curated Catalog upstream to proxy and cache curated packages through your Cloudsmith repository.
In the Cloudsmith console, go to your repository > Libraries tab, then add a new upstream and select ActiveState Curated Catalog as the upstream source.Proxy and cache packages from your ActiveState Curated Catalog (2026-10-15) · Oct 2026 · source -
Configure a hardened image upstream directly from the Cloudsmith UI without manually entering format or URL details.
In the repository settings, go to Upstreams > Hardened Images tab and select the hardened image source to proxy and cache.Hardened images tab for configuring upstreams (2026-07-15) · Jul 2026 · source -
Configure a Docker Hub upstream proxy in Cloudsmith without supplying your own Docker Hub credentials to get higher pull rate limits.
In the Cloudsmith console, go to your repository > Upstreams > Add Upstream > Docker Hub, and complete setup without entering credentials — Cloudsmith supplies a managed token automatically.Set up Docker Hub and DHI upstreams with Cloudsmith-managed authentication (2026-06-29) · Jun 2026 · source
Nix package support shipped Host, publish, and consume Nix packages through Cloudsmith repositories, with upstream proxying for Nix channels and native Nix tooling support, available via the web app, API, and CLI.
Also counts toward: Command-line interface, REST API, Web management console
release
- Supports pushing Nix packages via the Cloudsmith CLI (v1.21.0–v1.26.0). changelog · Oct 2026 · source · release history
-
Adds Nix package support, enabling
cloudsmith pushfor Nix packages.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ CLI v1.21.0 to v1.26.0: Nix support, Cargo and pnpm credential helpers, and repository administration from your terminal (2026-09-28) · Sep 2026 · source · release history - Adds the ability to push Nix packages directly from the CLI CLI v1.21.0 to v1.26.0: Nix support, Cargo and pnpm credential helpers, and repository administration from your terminal (2026-09-28) · Sep 2026 · source · release history
- Supports the Nix package format, enabling hosting of public or private Nix binary caches with Ed25519-signed packages and upstream proxying/caching against NixOS release channels. changelog · Aug 2026 · source · release history
- Adds Nix format repository support, enabling hosting of public or private Nix binary caches with Ed25519-signed packages. New format: Nix, with upstream support for NixOS (2026-08-24) · Aug 2026 · source · release history
- Supports upstream proxying and caching against NixOS release channels, so Nix clients can pull from Cloudsmith as a transparent cache in front of official NixOS channels. New format: Nix, with upstream support for NixOS (2026-08-24) · Aug 2026 · source · release history
docs
-
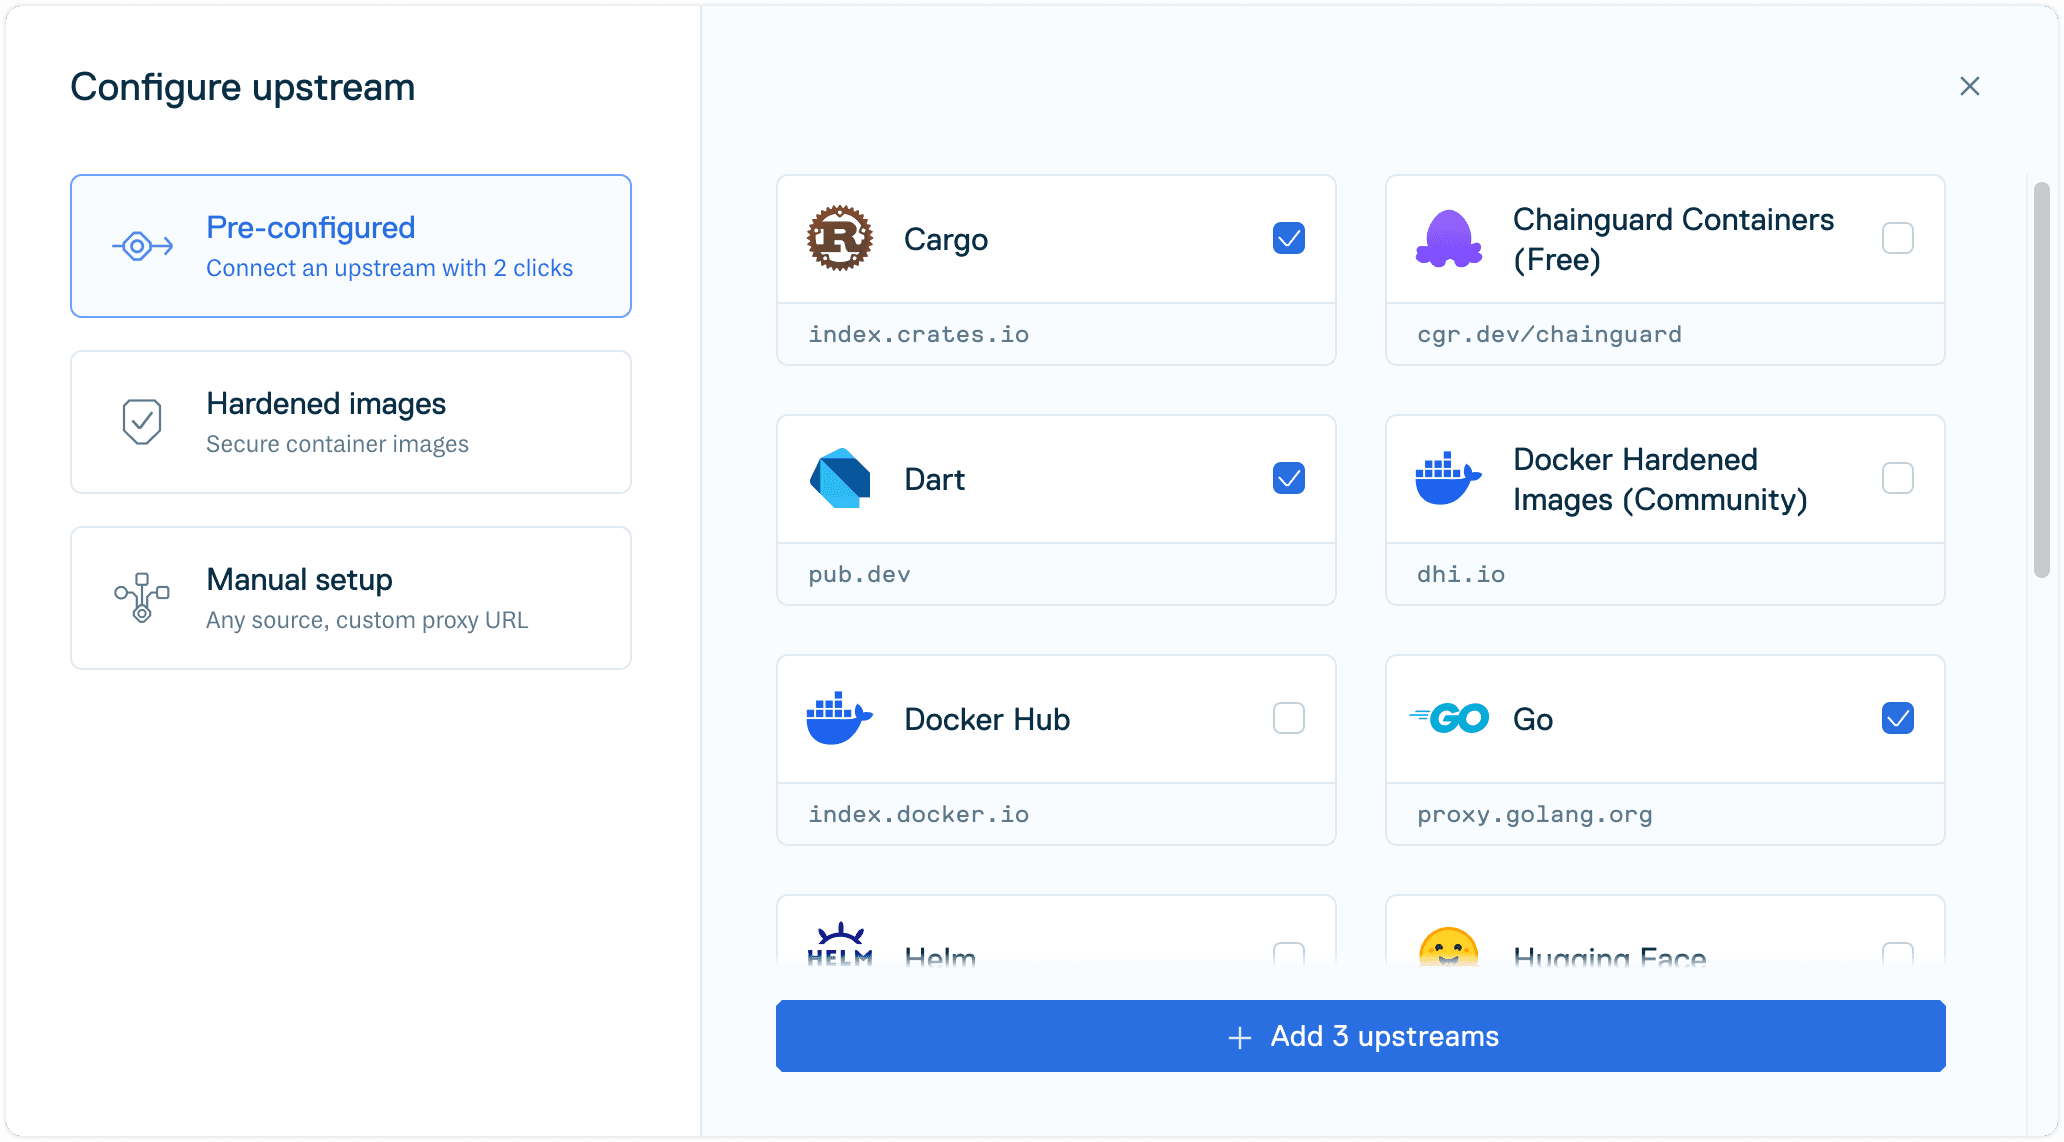
Nix upstreams are available in Early Access via the Cloudsmith web app, API, and CLI. 1 minute ago
 docs update · Sep 2026
· source
- The Nix format is available in Early Access. You can upload packages and manage Nix channel upstreams with the Cloudsmith web app, API, and CLI, or publish and consume packages with native Nix tooling. docs update · Sep 2026 · source
- Supported formats Nix repository Nix is a package manager used by NixOS. Nix packages are distributed as pre-built, content-addressed artifacts served from a binary cache. Cloudsmith supports hosting a public or private Nix binary cache. docs update · Aug 2026 · source
example
-
Push a Nix package to your Cloudsmith repository.
cloudsmith push nix <owner>/<repo> <package_path>CLI v1.21.0 to v1.26.0: Nix support, Cargo and pnpm credential helpers, and repository administration from your terminal (2026-09-28) · Sep 2026 · source
Cooldown policies shipped Holds newly published package versions in quarantine for a configurable delay period before making them available, reducing exposure to attacks on freshly released packages.
release 7 total
- Extends cooldown policies to Ruby gem packages, protecting supply chains from newly published versions that may carry malware or lack community scrutiny. changelog · Oct 2026 · source · release history
-
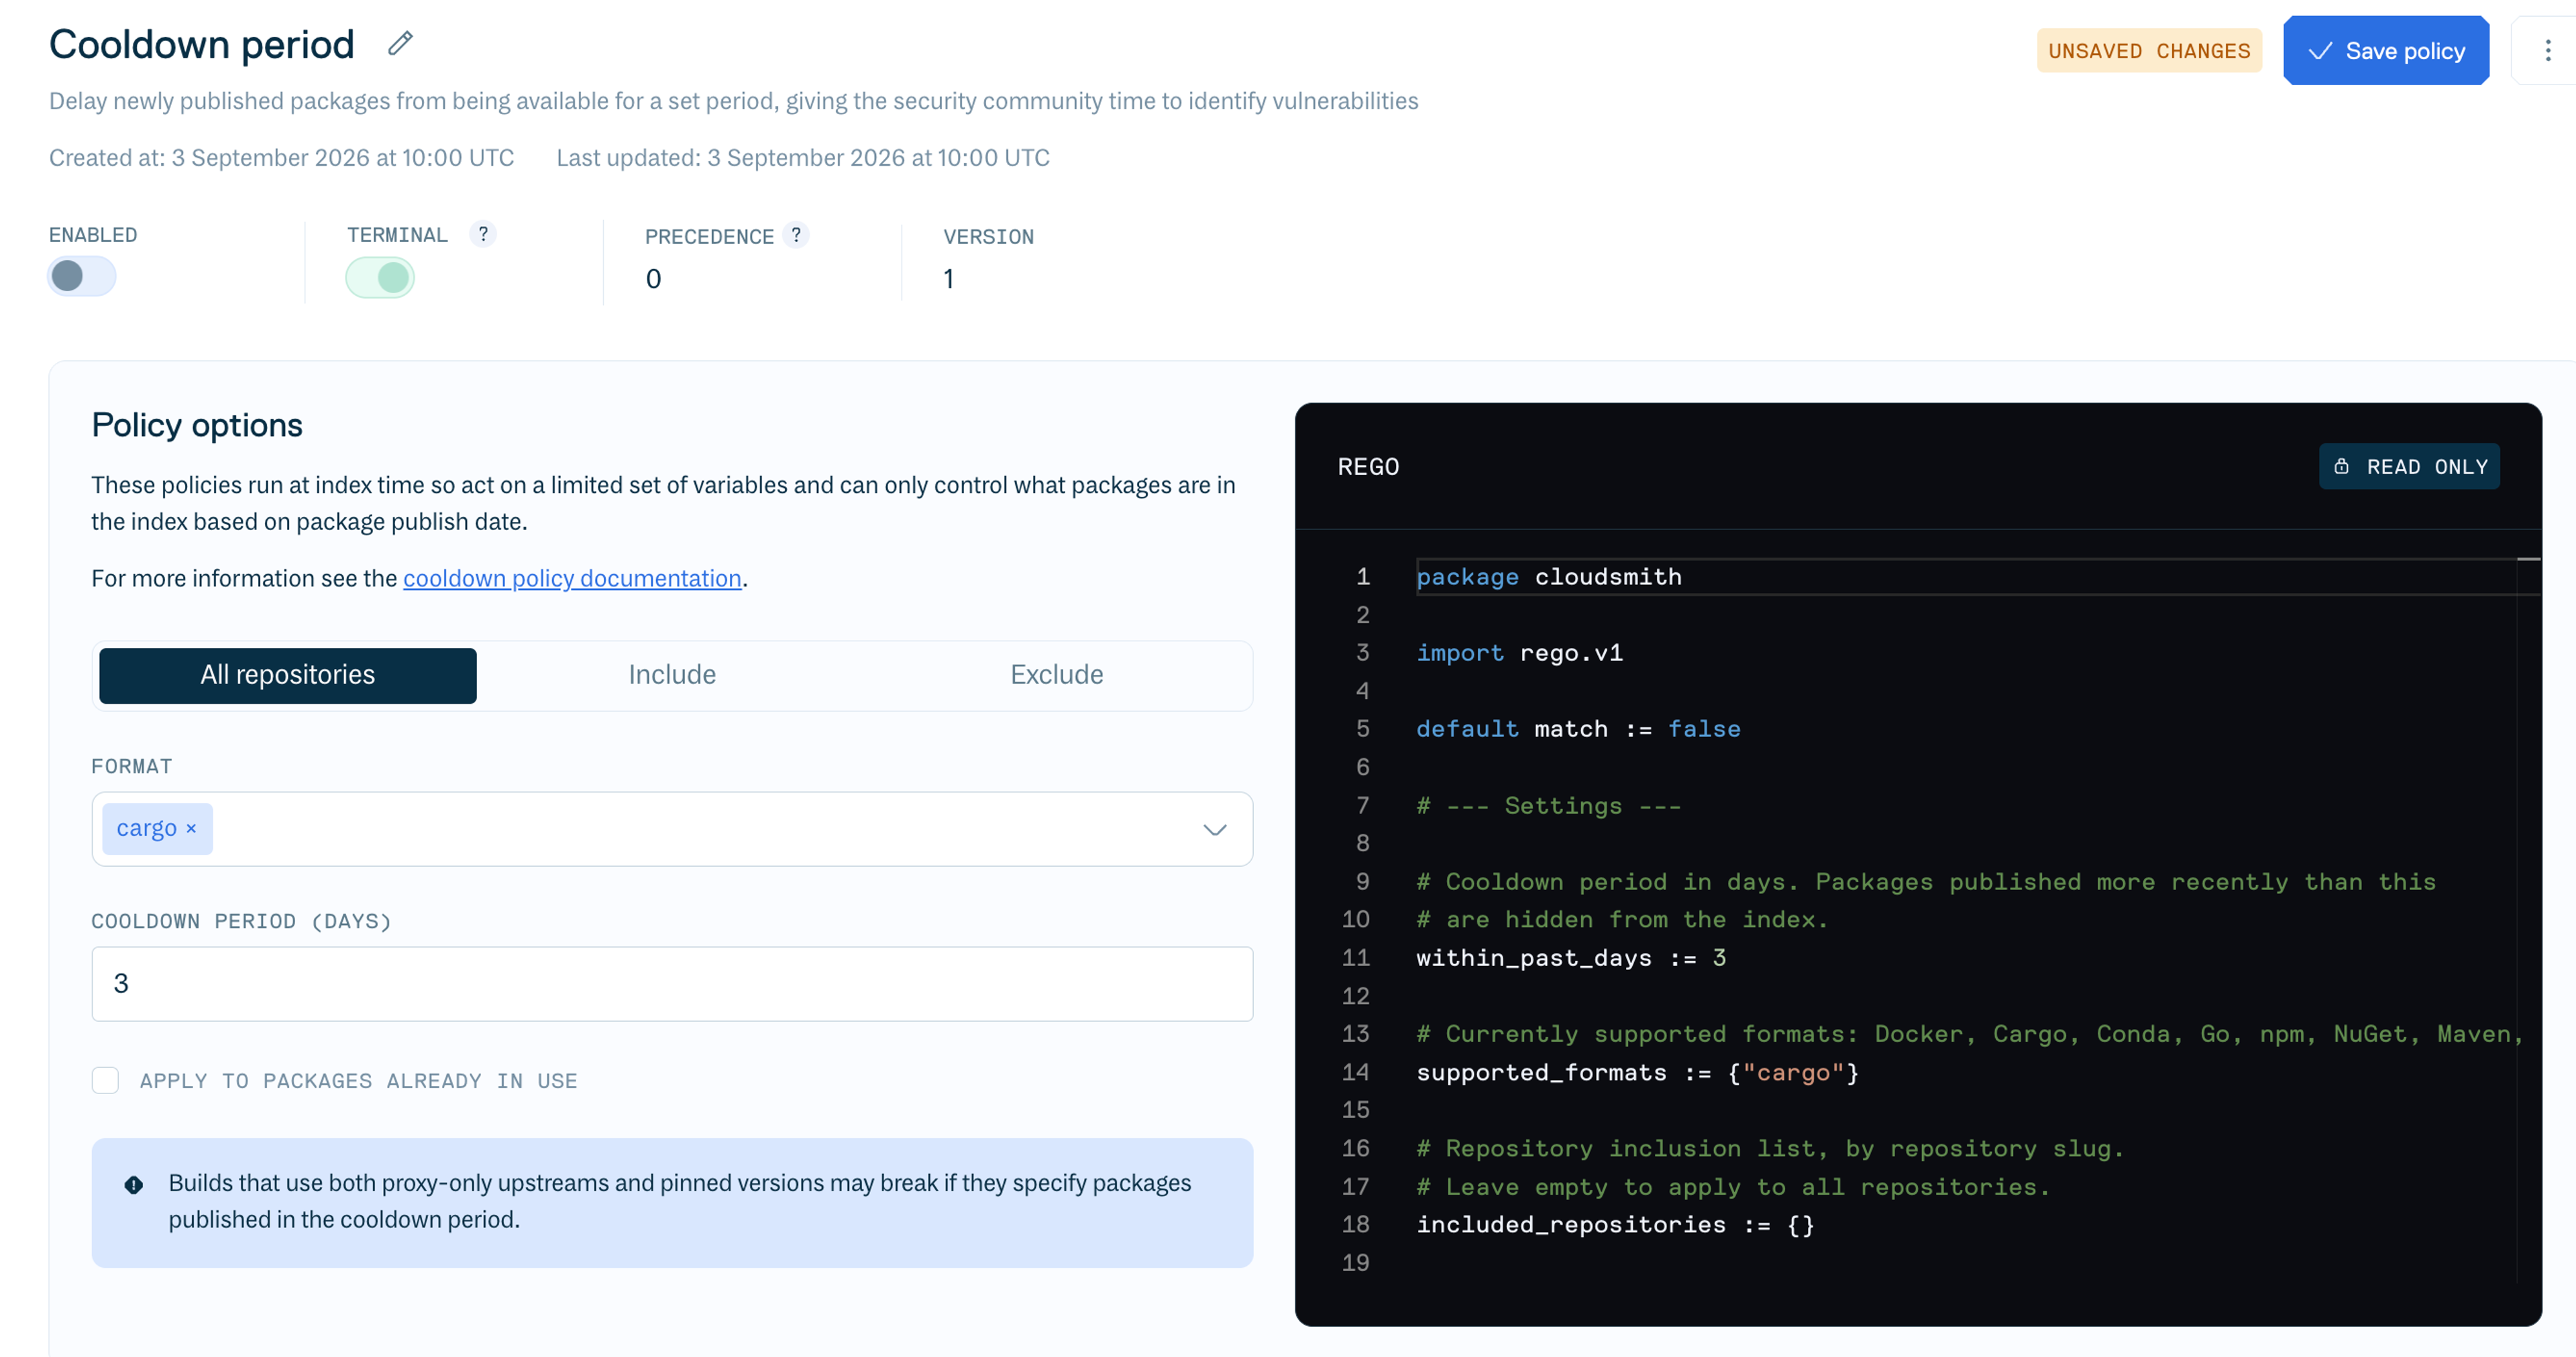
Adds Cargo to the list of package types supported by cooldown policies (npm, Python, Go, Maven, NuGet, Conda, Docker, and Cargo).
 Cooldown policies now support Cargo · Sep 2026
· source
· release history
- Extends cooldown policies to Cargo packages, blocking newly published versions from being consumed until a configured delay period has passed. Cooldown policies now support Cargo (2026-09-03) · Sep 2026 · source · release history
- Extends cooldown policies to Maven packages, enabling supply-chain protection against newly published versions that haven't undergone sufficient scrutiny. changelog · Jul 2026 · source · release history
- Supports cooldown policies for Maven packages, blocking newly published versions from being consumed until a configured delay period has elapsed. Cooldown policies now support Maven (2026-07-23) · Jul 2026 · source · release history
- Supports cooldown policies for NuGet packages, blocking newly published versions from being consumed until a configured quarantine period has elapsed. Cooldown policies now support NuGet (2026-07-07) · Jul 2026 · source · release history
docs
- Cooldown policies now support Conda and Docker You can now apply cooldown policies to Conda and Docker packages, protecting your supply chain from newly published versions that may carry malware or have not yet undergone sufficient community scrutiny… Aug 27 2026 Track downloads, token use, and client logs in the… changelog · Aug 2026 · source
Repository and package inspection via CLI shipped Allows users to list and inspect repositories and their contents directly from the command line.
Also counts toward: Command-line interface
release
- Adds the ability to list packages from connected repositories alongside your own packages in CLI v1.29.0. changelog · Oct 2026 · source · release history
-
Adds
connected_repositoriesfield to client log exports, listing every connected repository a package was served through so downloads can be traced back to their origin.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Trace downloads through connected repositories in client log exports (2026-10-01) · Oct 2026 · source · release history
docs
- The examples in this document are generic. Cloudsmith provides contextual setup instructions within each repository, complete with copy and paste snippets that have your workspace, repository, and RSA key pre-configured. seen Sep 2026 · source
- The examples in this document are generic. Cloudsmith provides contextual setup instructions within each repository, complete with copy and paste snippets with your workspace, repository, and RSA key pre-configured. docs update · Sep 2026 · source
- The examples in this document are generic. Cloudsmith provides contextual setup instructions within each repository, complete with copy and paste snippets with your workspace, repository, and RSA key pre-configured. docs update · Sep 2026 · source
example
-
Show the authenticated account for the current API key.
cloudsmith whoami -
List packages in a repository.
cloudsmith list packages my-org/my-repo -
List repositories for a namespace/owner.
cloudsmith list repos my-org
Docker credential helper shipped Handles Docker registry authentication automatically in the background so developers do not need to run manual login commands.
Also counts toward: CI/CD pipeline integration, Command-line interface
release
- Installs credential helpers in a location that survives package-manager upgrades, preventing accidental removal. CLI v1.30.0: Error reporting, TLS-intercepting proxy support, and a username and password login deprecation (2026-10-22) · Oct 2026 · source · release history
- CLI v1.21.0–v1.26.0 adds credential helpers for Cargo and pnpm, enabling automatic authentication against Cloudsmith repositories. changelog · Oct 2026 · source · release history
- Adds a Cargo credential helper so Rust projects authenticate to Cloudsmith repositories automatically. CLI v1.21.0 to v1.26.0: Nix support, Cargo and pnpm credential helpers, and repository administration from your terminal (2026-09-28) · Sep 2026 · source · release history
- Adds a pnpm credential helper so pnpm authenticates to Cloudsmith repositories automatically. CLI v1.21.0 to v1.26.0: Nix support, Cargo and pnpm credential helpers, and repository administration from your terminal (2026-09-28) · Sep 2026 · source · release history
- Introduces a Docker credential helper in the CLI to automatically authenticate to Cloudsmith registries. changelog · Jul 2026 · source · release history
-
New Docker credential helper automatically authenticates to Cloudsmith registries without manual
docker loginsteps. CLI v1.19.0: Authenticate automatically with OIDC and Docker credential discovery (2026-07-23) · Jul 2026 · source · release history
docs
- CLI v1.19.0: Authenticate automatically with OIDC and Docker credential discovery The Cloudsmith CLI now eliminates the need for static API keys in CI/CD pipelines by automatically discovering OpenID Connect (OIDC) credentials for all major CI/CD platforms and includes a Docker credential helper to automatically… changelog · Jul 2026 · source
SCIM group provisioning shipped Automatically synchronise Cloudsmith team membership with identity provider groups so users are added or removed when their IdP group membership changes.
release
- Promotes SCIM group provisioning to general availability on Ultra and Enterprise plans, automatically syncing Cloudsmith team membership when users are added or removed from mapped IdP groups. changelog · Oct 2026 · source · release history
- Automatically creates Cloudsmith teams if they do not exist during the next IdP sync SCIM group provisioning is now generally available · Sep 2026 · source · release history
- Adds SCIM 2.0 compliance to automatically provision Cloudsmith team membership based on identity provider (IdP) groups SCIM group provisioning is now generally available · Sep 2026 · source · release history
docs
- Trace downloads through connected repositories in client log exports A connected_repositories field in client log exports lists the connected repositories a package was served through, so you can trace a download back from the repository that served it… Oct 1 2026 SCIM group provisioning is now generally available You… changelog · Oct 2026 · source
Per-package audit trail shipped Provide a timestamped, per-package audit trail in the web app UI with actor and metadata details, supporting filtering by specific action types.
Also counts toward: Web management console
release
-
Adds Package logs in the Cloudsmith web app UI under Logs, providing a per-package audit trail with timestamp, action, actor, and metadata like package size and IP address
Track every change to your packages with package logs · Sep 2026
· source
· release history
- Enables filtering package logs by action (Copy, Delete, Hard delete, Move, Policy violation, Quarantine, Restore, Resync, Sync, Tags changed) to isolate specific events Track every change to your packages with package logs · Sep 2026 · source · release history
docs
- Download package vulnerability findings from the Cloudsmith web app Vulnerability and malicious package findings can now be exported as a JSON file directly from the web app… Sept 14 2026 Track every change to your packages with package logs Package logs are now available in the Cloudsmith web app, giving you a… changelog · Sep 2026 · source
example
-
Audit who made changes to a specific package and when — handy during an incident investigation.
In the Cloudsmith web app, open the repository, select the package, and open the 'Package Logs' tab to view the full per-package audit trail.changelog · Sep 2026 · source
Workspace usage limit controls shipped Set precise numerical usage limits for a workspace through the Settings tab, replacing slider controls that caused rounding errors.
release
- Workspace owners and managers can now type exact numerical values for usage limits on the workspace Settings tab under Usage limits, replacing imprecise sliders. changelog · Oct 2026 · source · release history
-
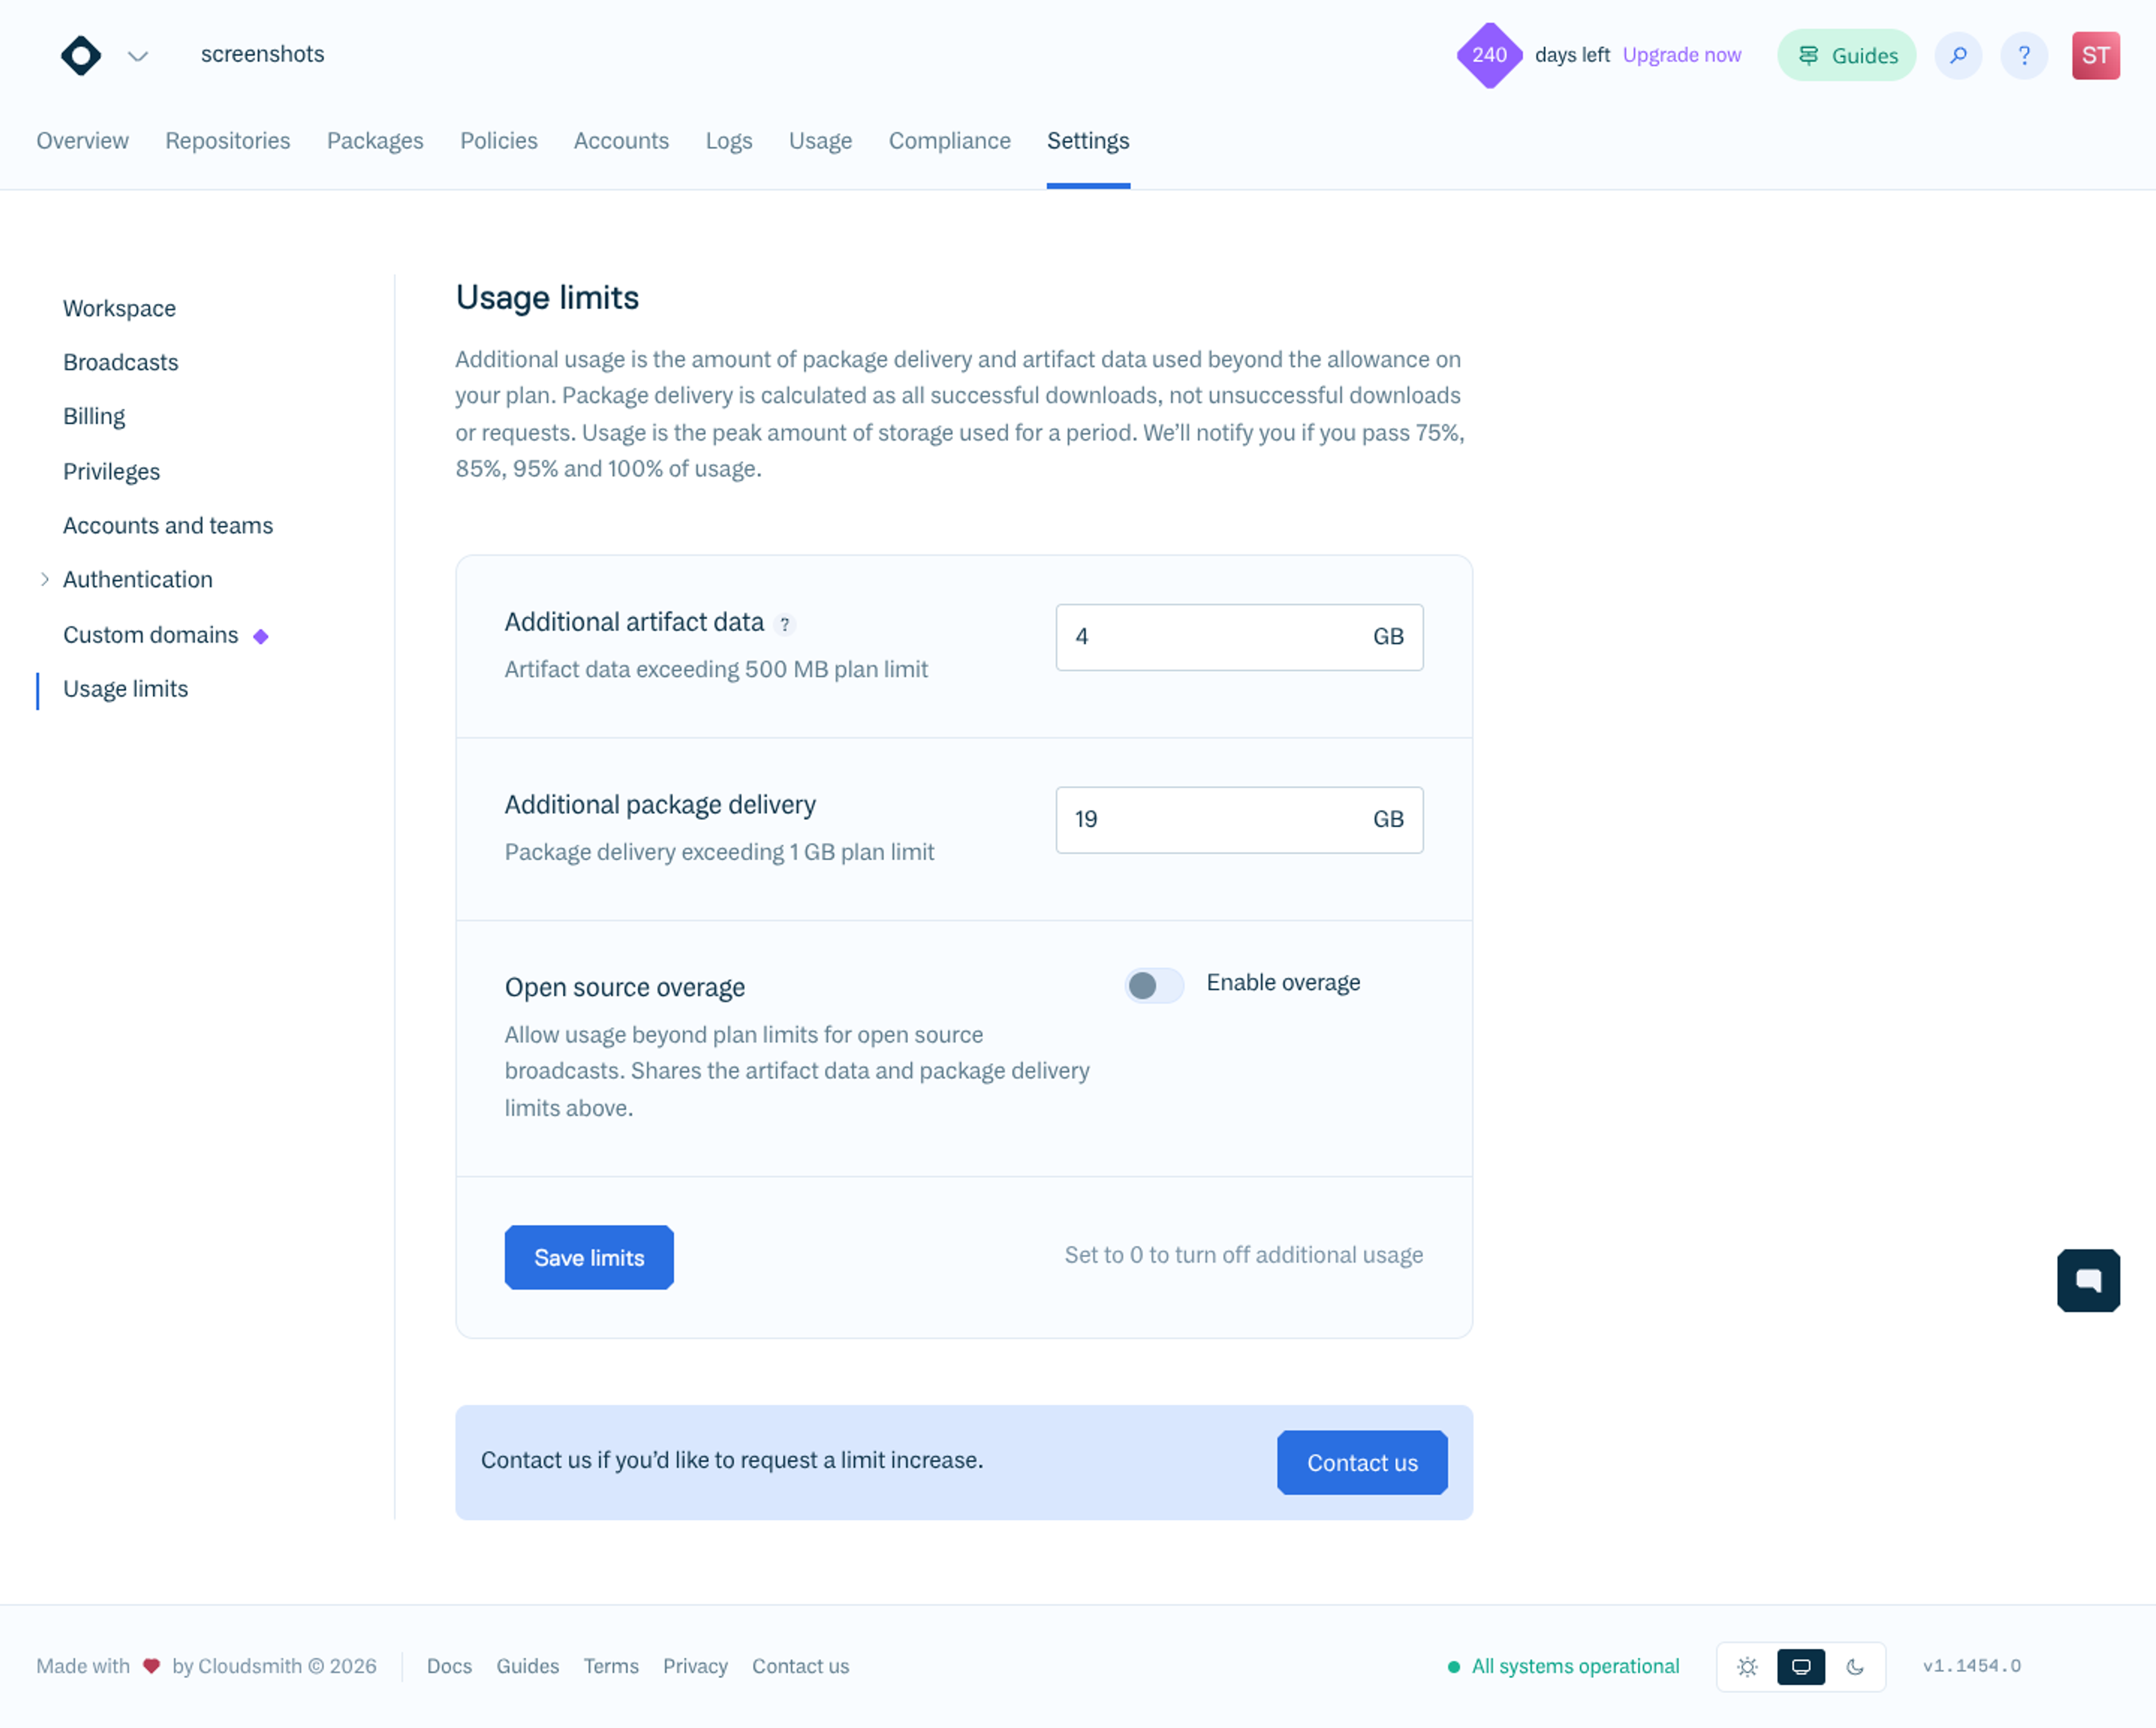
Enables typing exact numerical values for usage limits in the workspace Settings tab under Usage limits, replacing the former slider controls.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
 Set exact usage limits with numerical inputs (2026-10-21) · Oct 2026
· source
· release history
example
-
Set a precise usage limit for your workspace without rounding errors from slider controls.
In the Cloudsmith console, go to Workspace Settings > Usage limits and type an exact numerical value into the limit field.Set exact usage limits with numerical inputs (2026-10-21) · Oct 2026 · source
Cargo credential helper shipped Automatically authenticate to Cloudsmith Cargo registries without manual credential configuration, via a credential helper in the CLI.
release
- Installs credential helpers in a location that survives package-manager upgrades, preventing accidental removal. CLI v1.30.0: Error reporting, TLS-intercepting proxy support, and a username and password login deprecation (2026-10-22) · Oct 2026 · source · release history
- Adds automatic authentication for Cargo via a credential helper CLI v1.21.0 to v1.26.0: Nix support, Cargo and pnpm credential helpers, and repository administration from your terminal (2026-09-28) · Sep 2026 · source · release history
example
-
Configure Cargo to use Cloudsmith's credential helper for authentication.
cargo config set registry.<registry>.credential-helper cloudsmithCLI v1.21.0 to v1.26.0: Nix support, Cargo and pnpm credential helpers, and repository administration from your terminal (2026-09-28) · Sep 2026 · source
Client log metadata visibility shipped Capture and expose format-specific package metadata fetches in client logs alongside direct downloads to provide full traffic visibility.
release
-
Client logs in the Cloudsmith web app now capture format-specific metadata across every supported package format, exposing package metadata fetches alongside direct package downloads for full traffic visibility.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
 Client logs now show the full request chain behind a package download (2026-09-25) · Sep 2026
· source
· release history
- Client logs now capture format-specific metadata across every package format Cloudsmith supports Client logs now show the full request chain behind a package download (2026-09-25) · Sep 2026 · source · release history
example
-
Verify package metadata visibility in web app client logs to audit traffic.
Review the client logs in the Cloudsmith web app for a workspaceClient logs now show the full request chain behind a package download (2026-09-25) · Sep 2026 · source
Granular role-based access control shipped Grant workspace members read-only access to specific sensitive data categories (billing, usage, OIDC) without assigning elevated Manager or Owner roles.
Also counts toward: Role-based access control
release
- Lets workspace owners grant members read-only access to billing, usage, and OIDC data individually, without assigning the Manager or Owner role. changelog · Sep 2026 · source · release history
docs
- The following privileges can be granted to workspace members: View workspace billing information. View workspace usage data, including artifact data and package delivery quotas. View workspace OpenID Connect (OIDC) settings. 4 days ago seen Sep 2026 · source
example
-
Give a finance or compliance team member visibility into billing and OIDC configuration without elevating their role to Manager or Owner.
In the Cloudsmith web app, go to Workspace Settings > Members, select the member, and enable the individual 'Billing', 'Usage', or 'OIDC' read-only privilege toggles separately.changelog · Sep 2026 · source
Terraform provider shipped Allows Cloudsmith repositories, upstreams, and policies to be declared and managed as Terraform resources alongside other infrastructure.
Also counts toward: Terraform provider
release
-
Enables creation of cooldown policies for Cargo via the Cloudsmith API, Terraform provider, and web app.
Cooldown policies now support Cargo · Sep 2026
· source
· release history
-
New
cloudsmith_connected_repositoryTerraform resource enables defining connected repository configurations alongside other Cloudsmith infrastructure as code. Create and manage connected repositories with Terraform (2026-06-15) · Jun 2026 · source · release history
example
-
Declare a connected repository in Terraform to manage upstream proxy or mirroring configurations alongside the rest of your Cloudsmith infra.
resource "cloudsmith_connected_repository" "example" { # configuration fields here }Create and manage connected repositories with Terraform (2026-06-15) · Jun 2026 · source
CLI crash reporting shipped Sends anonymous reports of unexpected errors to Cloudsmith by default so crashes are detected without requiring manual support tickets.
release
- CLI v1.30.0 now sends anonymous error reports to Cloudsmith by default so crashes can be identified without a support ticket. changelog · Oct 2026 · source · release history
- Sends anonymous reports of unexpected errors to Cloudsmith by default, allowing crash detection without manual support tickets. CLI v1.30.0: Error reporting, TLS-intercepting proxy support, and a username and password login deprecation (2026-10-22) · Oct 2026 · source · release history
CLI TLS-intercepting proxy support shipped Allows the CLI to operate through enterprise TLS-intercepting proxies without disabling certificate verification.
Also counts toward: Command-line interface
release
- Adds TLS-intercepting proxy support to the Cloudsmith CLI v1.30.0, enabling connections through TLS-intercepting proxies without disabling certificate verification.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ changelog · Oct 2026 · source · release history
- Supports TLS-intercepting proxies without disabling certificate verification, enabling CLI use in enterprise environments with SSL inspection.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ CLI v1.30.0: Error reporting, TLS-intercepting proxy support, and a username and password login deprecation (2026-10-22) · Oct 2026 · source · release history
Username and password login deprecation shipped Username and password authentication via `cloudsmith login` and `cloudsmith token` is deprecated and will stop working on November 20, 2026.
release
-
Username and password login via
cloudsmith loginandcloudsmith tokenstops working on November 20, 2026 — scripts and CI jobs using these commands must switch to API key authentication before that date. changelog · Oct 2026 · source · release history -
Username and password login via
cloudsmith loginandcloudsmith tokenis deprecated and stops working on November 20, 2026. CLI v1.30.0: Error reporting, TLS-intercepting proxy support, and a username and password login deprecation (2026-10-22) · Oct 2026 · source · release history
Hugging Face model support documented Host, publish, and consume Hugging Face AI models through Cloudsmith repositories, with support for the Hugging Face commit-based snapshot model.
docs
-
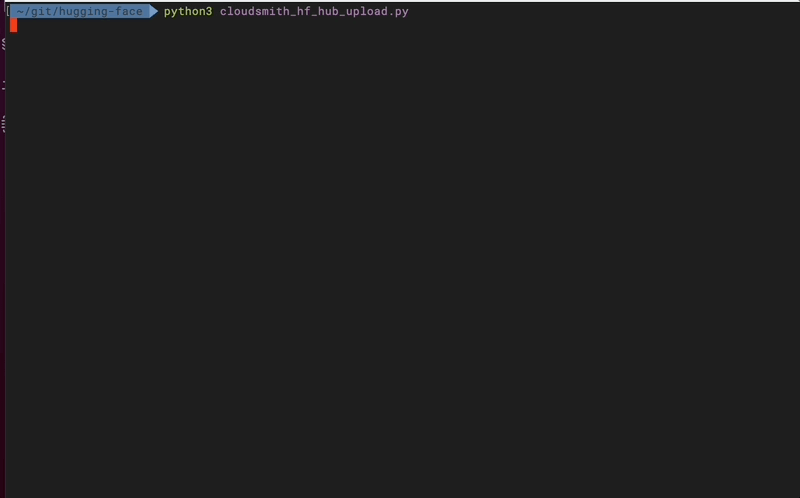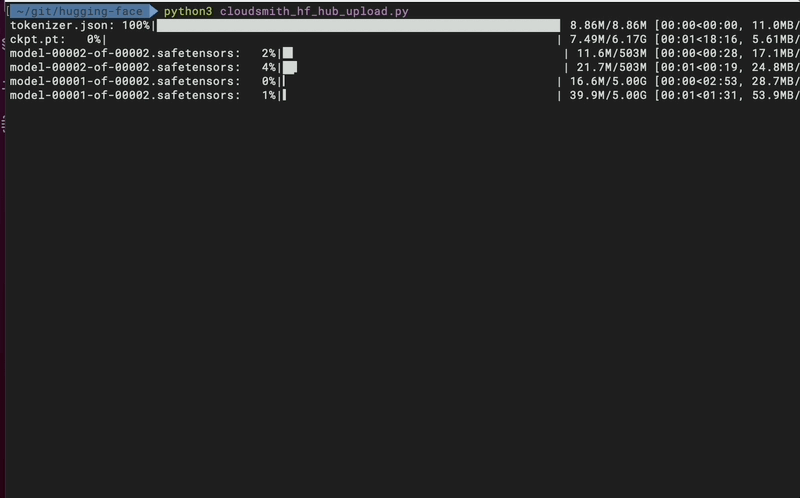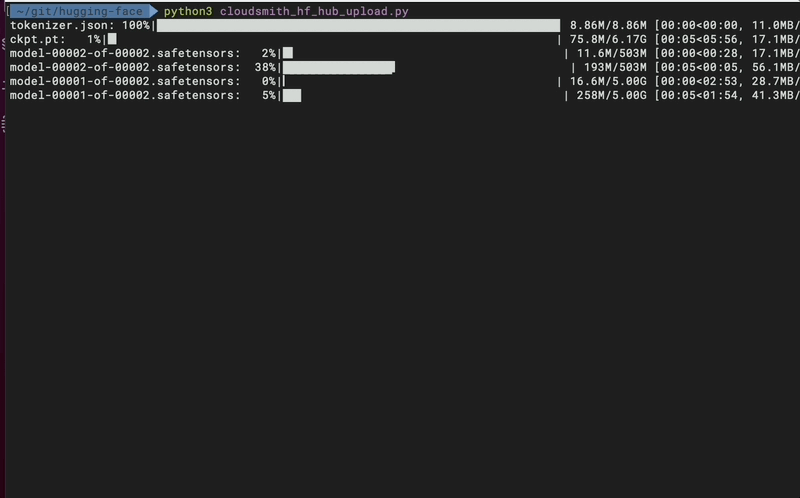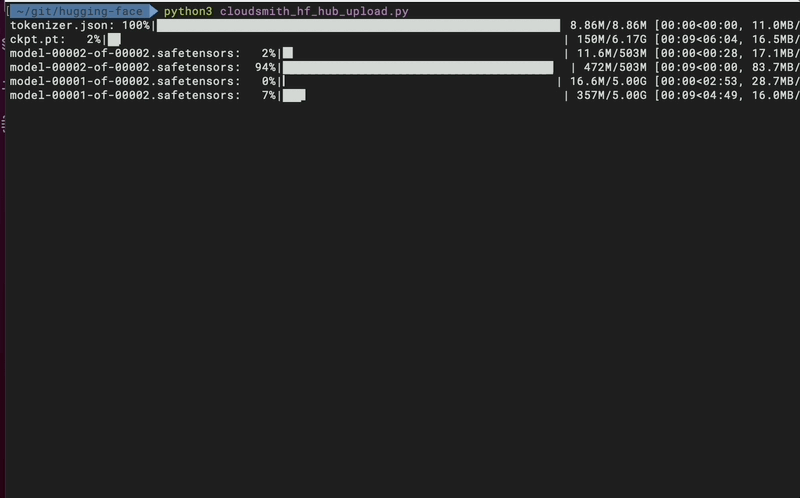
Hugging Face is an open-source platform and ecosystem for building, sharing, and deploying AI models, especially in the field of natural language processing (NLP) and generative AI. AI models In the Hugging Face ecosystem, a commit represents a complete snapshot of a repository at a specific point in time.
 docs update · Oct 2026
· source
- - such as Docker, Python, Maven, npm, Helm, AI models, and more - and integrates with CI/CD systems, developer workflows, and security tools. Artifacts are delivered through a global Package Delivery Network (PDN) for fast, reliable access anywhere in the world. seen Oct 2026 · source
CLI self-update shipped Allows the CLI to upgrade itself to the latest version without requiring external package managers or scripts.
Also counts toward: Command-line interface
release
- Adds a built-in self-update capability to the Cloudsmith CLI (v1.27.0+) so the CLI can upgrade itself without external tooling. changelog · Oct 2026 · source · release history
example
-
Upgrade the Cloudsmith CLI to the latest version using its built-in self-update, then switch to a specific workspace context.
cloudsmith update cloudsmith --workspace <workspace-slug> <subcommand>changelog · Oct 2026 · source
CLI workspace context management shipped Provides a command-line flag to read and apply workspace-specific settings directly from the CLI.
Also counts toward: Command-line interface
release
-
Adds a
--workspaceoption to the Cloudsmith CLI to read workspace settings from the command line. changelog · Oct 2026 · source · release history
example
-
Upgrade the Cloudsmith CLI to the latest version using its built-in self-update, then switch to a specific workspace context.
cloudsmith update cloudsmith --workspace <workspace-slug> <subcommand>changelog · Oct 2026 · source
Connected repository download tracing shipped Client log exports include a connected_repositories field that identifies which connected repositories a package was served through, enabling download provenance to be traced across repository chains.
Also counts toward: CSV data export, JSON data export
release
-
Adds the
connected_repositoriesfield to JSON and CSV client log exports to list repositories through which a package was served. Trace downloads through connected repositories in client log exports · Oct 2026 · source · release history
docs
- Trace downloads through connected repositories in client log exports A connected_repositories field in client log exports lists the connected repositories a package was served through, so you can trace a download back from the repository that served it… Oct 1 2026 SCIM group provisioning is now generally available You… changelog · Oct 2026 · source
Repository GPG key and access management via CLI shipped Manage repository GPG keys and access privileges directly from the command line.
Also counts toward: Command-line interface
release
- Adds repository administration commands for managing GPG keys and access privileges CLI v1.21.0 to v1.26.0: Nix support, Cargo and pnpm credential helpers, and repository administration from your terminal (2026-09-28) · Sep 2026 · source · release history
example
-
Manage GPG keys for a repository directly from the terminal.
cloudsmith repo gpg-key list <owner>/<repo>CLI v1.21.0 to v1.26.0: Nix support, Cargo and pnpm credential helpers, and repository administration from your terminal (2026-09-28) · Sep 2026 · source
Broadcasts distribution shipped Distribute software packages to end-users through a customizable and secure interface with download tracking and entitlement token usage visibility.
release
- Adds download tracking, entitlement token usage, and client log visibility directly within the Broadcasts app. changelog · Aug 2026 · source · release history
docs
-
Broadcasts help you distribute your software packages to your end-users through a customizable, secure, and user-friendly interface. It allows you to create a seamless experience for your customers, making it feel as though they are interacting directly with your own infrastructure, rather than a third-party service.
docs update · Aug 2026
· source
Artifact storage regions shipped Store artifacts in geographically distributed regions, including Mumbai, to reduce download latency for users and CI/CD pipelines.
release
- Adds Mumbai as a supported artifact storage region, reducing download latency for users and CI/CD pipelines in India. changelog · Oct 2026 · source · release history
npm and pnpm install performance shipped Reduce client request count and upstream lookups per npm repository, speeding up npm and pnpm installs without requiring configuration changes.
release
- Reduces pnpm client request count against Cloudsmith and reduces upstream lookups per npm repository, speeding up npm installs with no configuration changes required. changelog · Oct 2026 · source · release history
npm provenance and attestation support shipped Serve npm attestations and signing-key APIs from Cloudsmith npm registries so that clients can verify package provenance the same way they do against the upstream npm registry.
Also counts toward: REST API
release
- Cloudsmith's npm registry now serves npm attestations and signing-key APIs, enabling npm provenance verification through Cloudsmith just as it works against the upstream registry. changelog · Oct 2026 · source · release history
CLI SSO session resilience shipped Maintains active single sign-on sessions during temporary network interruptions without requiring re-authentication.
release
- Adds SSO session resilience to the Cloudsmith CLI, keeping single sign-on sessions alive through temporary network failures. changelog · Oct 2026 · source · release history
Terraform credential helper shipped Provides a command-line helper that automatically authenticates Terraform to Cloudsmith registries without persisting tokens.
Also counts toward: Command-line interface
release
- Adds a Terraform credential helper to the Cloudsmith CLI that authenticates Terraform to Cloudsmith registries without storing a token. changelog · Oct 2026 · source · release history
pnpm credential helper shipped Automatically authenticate to Cloudsmith npm-compatible registries for pnpm without manual credential configuration, via a credential helper in the CLI.
release
- Adds automatic authentication for pnpm via a credential helper CLI v1.21.0 to v1.26.0: Nix support, Cargo and pnpm credential helpers, and repository administration from your terminal (2026-09-28) · Sep 2026 · source · release history
Bug bounty programme shipped Offers a public bug bounty platform where security researchers can submit vulnerability reports about Cloudsmith's own services.
release
-
New bug bounty platform launched at
bounties.cloudsmith.comfor security researchers to submit vulnerability reports. changelog · Aug 2026 · source · release history
PEP-658 metadata-only resolution shipped Serves Python package metadata separately from package archives so dependency resolution tools can work without downloading full packages.
release
- Supports PEP-658 on the Simple API, enabling Python package clients (pip, uv, etc.) to retrieve only package metadata during dependency resolution instead of downloading full package archives. Speed up Python builds with PEP-658 support (2026-07-02) · Jul 2026 · source · release history
Package metadata labels shipped Lets teams attach arbitrary key-value labels to any package to record build provenance, compliance evidence, or cost attribution alongside the artifact.
release
- Enables attaching custom key-value metadata to any package to store structured contextual data such as CI build info, Git provenance, compliance evidence, and cost attribution directly alongside the artifact. Enrich packages with custom metadata (2026-06-16) · Jun 2026 · source · release history
OCI repository support documented Host and distribute OCI images and generic artifacts through Cloudsmith OCI-compatible repositories, including support for ORAS-based uploads.
docs
- OCI repository Differences from the OCI image and distribution specification Naming differences Upload an Generic artifact with ORAS Entitlement Tokens , User Credentials and API-Keys should be treated as secrets, and you should ensure that you do not commit them in configurations files along with source code or… seen Oct 2026 · source
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
23 commands for Cloudsmith, each with where it came from. This tool has no source analysis yet, so there is no option reference and no captured run beside them.
No command matches.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for Cloudsmith, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Cloudsmith puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Commercials
pricing & packaging history · Cloudsmith vendor page19 readings of Cloudsmith's pricing page since May 2023, with 2 relaunches of its plan lineup and 10 changes to what its plans include — each one dated, compared with the reading before it, and explained for someone buying the tool.
Pricing and packaging history is included with Researcher and Business. See how every vendor we track sells, and how that has changed over time, using data we don't publish anywhere else.
See plans → Already subscribed? Sign in →Plans by offering
Each offering on the pricing page links to its own page of plans, read at its latest capture.
Plan relaunches
Plans, prices and descriptions are quoted from the vendor's own pricing page as we read it on each date. A plan missing from a later reading is shown as no longer listed on the page — a statement about the page, not the product. Readings that failed to show any plans are left out rather than read as a change.
Website history
cloudsmith.com, every changeCloudsmith's home page and 8 more pages as they looked each month from August 2021 to October 2026: 19 renders, 7 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Coverage
Missing something? Tell us
What Cloudsmith connects to, runs on and detects, read from its release notes and docs. So far: 4 new integrations, 1 new supported platform.
5 changes, tracked since Oct 4, 2026.
-
Oct 282026
new Mumbai storage region
Mumbai is now a supported storage region Store artifacts closer to your users and CI/CD pipelines in India, so downloads are faster…
-
Oct 222026
new Hugging Face repository format support
Hugging Face is an open-source platform and ecosystem for building, sharing, and deploying AI models, especially in the field of natural language processing (NLP) and generative AI.
-
Oct 152026
new ActiveState Curated Catalog upstream
Cloudsmith now supports ActiveState Curated Catalog upstreams, with configuration built into the Libraries tab.
-
Oct 42026
new Nix package format support in Cloudsmith CLI
you can now push Nix packages
-
Oct 42026
new Cargo and pnpm credential helpers in Cloudsmith CLI
let Cargo and pnpm authenticate automatically with credential helpers
Model providers & gateways 1
Languages & runtimes 2
Other 2
Other 1
Nothing first seen in this window. That doesn't mean Cloudsmith shipped nothing, only that we found no record of it.
How we count
Read from 9 of 56 release notes and docs updates we hold for Cloudsmith. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through Cloudsmith's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
56 entries
No entries match these filters.
- October 202612
- September 202616
- August 202612
- July 202610
- June 20266
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →