Sublime Security
Platform v1.90.133 (Attack Score Flash) (2026-10-27) commercialThe section your link pointed to isn't on Sublime Security's page any more, so we've brought you to the top.
Sublime Security is an email security platform that detects and blocks phishing, malware, and other email-based threats using customizable, logic-based detection rules.
type.inbound and beta.attack_score_flash().verdict in ("malicious", "potentially_malicious")
type.inbound and beta.attack_score_flash().verdict == "spam"
Summary
Sublime Security is a commercial, AI-powered email security platform run as SaaSSaaSSoftware delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally., protecting Microsoft 365 and Google Workspace environments (with IMAP and API ingestion also supported) for security teams who need to block phishing, BEC, and malware without staffing a full detection-engineering effort. It's built on a programmable detections engine that evaluates messages with its own query language (MQLMQLA query language created by Microsoft for hunting across telemetry in Microsoft 365 Defender, letting cyber tools express complex behavioral detections in a structured, readable syntax.) and can quarantine mail, fire webhooks, or insert warning banners, while its AI agents, ADÉ and ASA, write and backtest new detections and triage user-reported messages automatically. That combination of packaged protection with an underlying engine teams can extend themselves sets it apart from simpler filtering add-ons, and puts it closer to a platform for SOCSOCA security operations center, the team or function that monitors threats, investigates alerts and coordinates incident response. Its work can be internal, outsourced or shared. analysts and detection engineers than a plug-and-play filter. Recent work adds sandbox detonation via CrowdStrike Falcon and deeper Falcon SIEMSIEMSecurity information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents./SOARSOARSecurity orchestration, automation and response, coordinating incident workflows across tools. Playbooks can gather evidence, assign work or carry out approved response actions. integration.
Sublime Security is an email security platform that detects and blocks phishing, malware, and other email-based threats using customizable, logic-based detection rules.
How Sublime Security helps
Is a suspicious message actually malicious, or safe to ignore?
detonates the message in an isolated sandbox on demand and returns a verdict of malicious, suspicious, or benign, with a live-updating analysis view and a full behavioral report of indicators, network activity, and dropped files one click away
Which reported emails are real misses that need a new detection, and which are noise?
triages every user-reported and flagged message automatically, gives reporters a plain-language explanation of the verdict, and hands confirmed misses to the detection-writing agent to build coverage from
Why did this message get quarantined, blocked, or flagged?
every detection is written in a readable query language, so the specific rule and logic that matched a message can be inspected rather than taken on faith
How much of my flagged mail is actually an attack versus marketing and newsletters clogging the queue?
separates high-volume non-malicious mail into its own view using a machine-learning bulk-mail score, and learns per-user, per-sender preferences from folder moves to route similar mail automatically going forward
Has anyone outside my team touched my mail environment, and when?
logs every vendor support session with the account, role, and duration, shows a live banner during any active session, and keeps an exportable audit trail admins can review at any time
Are my child organizations licensed and provisioned the way they should be?
lists every child organization with its license and usage data and lets an admin apply or change licensing individually or in bulk across up to 200 organizations at once
Languages
Features
Built from Sublime Security's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
What Sublime Security offers you
- ML-based detection3
- REST API3
- Administrative audit log1
- Command-line interface1
- CSV data export1
- Role-based access control1
- SIEM forwarding1
- User-defined detection rules1
- Web management console1
No capabilities match.
Email threat detection and triage 1 capability Sublime Security's core function is identifying malicious, suspicious, and unwanted email and presenting it to analysts in prioritised queues. Dedicated views separate messages needing action from those matching rules or filters, so analysts always know what requires attention.
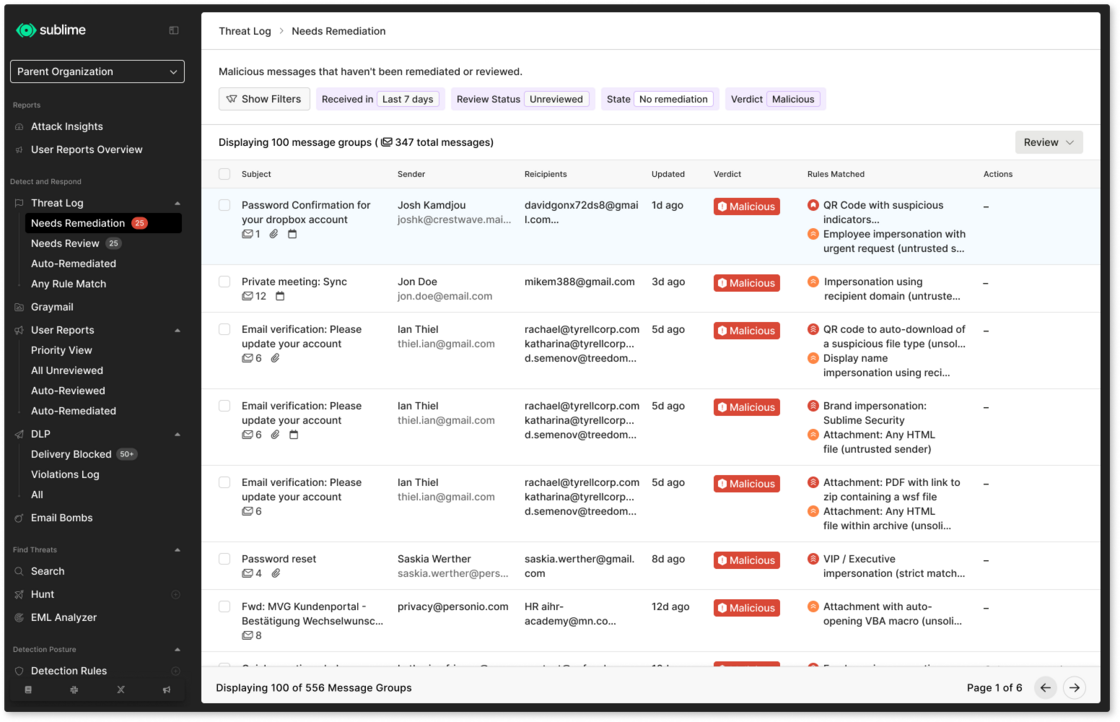
Navigation: Needs Remediation and Any Rule Match views verified Organises flagged messages into a Needs Remediation queue for actionable items and a separate Any Rule Match view for broader review.
release 11 total
-
Adds a message count badge to the Needs Review Threat Log view so unreviewed messages are always visible at a glance.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
 Platform v1.90.8 (Flexible Threat Log Views) (2026-10-19) · Oct 2026
· source
· release history
- Updates default filters: Needs Remediation opens on unreviewed Malicious messages with no remediation actions applied; Needs Review opens on Spam, Unknown, and Suspicious messages. Platform v1.90.8 (Flexible Threat Log Views) (2026-10-19) · Oct 2026 · source · release history
- Makes the State filter in Needs Remediation adjustable, letting analysts switch to states like auto-remediated or mixed without leaving the view. Platform v1.90.8 (Flexible Threat Log Views) (2026-10-19) · Oct 2026 · source · release history
- Makes the Verdict filter in Needs Review adjustable, letting analysts find messages with any verdict inside the same view. Platform v1.90.8 (Flexible Threat Log Views) (2026-10-19) · Oct 2026 · source · release history
-
GET
/v0/message-groups: param verdict__is_not (query) added︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ generated · Sep 2026 · source · release history - The Flagged view has been replaced; Needs Remediation is its closest equivalent for reviewing messages awaiting action. Platform v1.86 (Advanced Graymail Protection - Beta) (2026-07-16) · Jul 2026 · source · release history
example
-
Inspect Malicious-verdict messages directly from the Needs Review view by changing the Verdict filter.
In the Dashboard, go to Threat Log > Needs Review, then open the Verdict filter and select 'Malicious'.Platform v1.90.8 (Flexible Threat Log Views) (2026-10-19) · Oct 2026 · source -
Review all auto-remediated messages without leaving the Needs Remediation view by switching the State filter.
In the Dashboard, go to Threat Log > Needs Remediation, then open the State filter and select 'auto-remediated'.Platform v1.90.8 (Flexible Threat Log Views) (2026-10-19) · Oct 2026 · source -
Set the global metadata retention to a specific duration via the admin console.
Navigate to Admin > Account > Full Message Retention and set the desired value.Platform v1.84.93 (Configure retention for message metadata) (2026-05-26) · May 2026 · source
api
-
GET /v0/user-reports· source · full API surface -
POST /v0/message-groups/review· source · full API surface -
GET /v0/messages/groups/{id}/action-state· source · full API surface -
GET /v0/message-groups/search· source · full API surface -
GET /v0/rules/{id}/rule-history· source · full API surface
Graymail management 2 capabilities The cyber tool classifies high-volume non-malicious mail separately from threats and routes it automatically without analyst involvement. It also learns individual user preferences over time to reduce repeated manual sorting.
Graymail detection and automation verified Detects marketing mail and newsletters using an ML model and automatically routes them to a Promotions folder, keeping them out of the threat queue.
Also counts toward: ML-based detection
release 10 total
- Adds the Remediate graymail flagged messages Automation to route detected graymail to Promotions Platform v1.87 (Advanced Graymail Protection - GA) (2026-07-28) · Jul 2026 · source · release history
- Adds Advanced Graymail Protection (GA) to identify and manage marketing emails, newsletters, and subscription content across Microsoft 365 and Google Workspace. Platform v1.87 (Advanced Graymail Protection - GA) (2026-07-28) · Jul 2026 · source · release history
- New Rule Fuzzy Attack Score: Advanced Graymail Detection extends graymail detection coverage, designed to pair with the included Automation. Platform v1.87 (Advanced Graymail Protection - GA) (2026-07-28) · Jul 2026 · source · release history
- Adds the Fuzzy Attack Score: Advanced Graymail Detection Rule paired with the new Automation Platform v1.87 (Advanced Graymail Protection - GA) (2026-07-28) · Jul 2026 · source · release history
- New Remediate graymail flagged messages Automation routes detected graymail to Promotions automatically. Platform v1.87 (Advanced Graymail Protection - GA) (2026-07-28) · Jul 2026 · source · release history
- New Graymail Automation enables automatic routing, triaging, and management of detected graymail via the included Remediate graymail flagged messages automation. Platform v1.86 (Advanced Graymail Protection - Beta) (2026-07-16) · Jul 2026 · source · release history
example
-
Automatically filter marketing and newsletter emails into the Promotions folder using the new workflow.
In Admin → Settings, activate Automation: "Remediate graymail flagged messages" and Rule: "Fuzzy Attack Score: Advanced Graymail Detection"Platform v1.87 (Advanced Graymail Protection - GA) (2026-07-28) · Jul 2026 · source -
Activate automated graymail remediation to automatically route and manage detected graymail without manual triage.
In the console, activate the Rule 'Fuzzy Attack Score: Advanced Graymail Detection' and the Automation 'Remediate graymail flagged messages'.Platform v1.86 (Advanced Graymail Protection - Beta) (2026-07-16) · Jul 2026 · source -
Enable automatic handling of identified graymail messages.
Activate the Automation `"Remediate graymail flagged messages"` in the Admin panel.Platform v1.86 (Advanced Graymail Protection - Beta) (2026-07-16) · Jul 2026 · source -
Review high-volume non-malicious messages in a dedicated view separate from spam.
In the Sublime Platform, navigate to the `Graymail View` to see detected graymail.Platform v1.86 (Advanced Graymail Protection - Beta) (2026-07-16) · Jul 2026 · source
api
-
POST /v0/message-groups/move-to-graymail· source · full API surface -
POST /v0/messages/attack_score· source · full API surface
Graymail user preference learning shipped Watches how individual users move messages between folders and applies those preferences automatically to future deliveries from the same senders.
release
- New Graymail User Preferences feature (Admin → Account) learns from users moving messages into or out of Promotions or Junk/Spam and applies sender-level preferences to future messages. Platform v1.87 (Advanced Graymail Protection - GA) (2026-07-28) · Jul 2026 · source · release history
- Enables Graymail User Preferences under Admin → Account so Sublime learns user move patterns Platform v1.87 (Advanced Graymail Protection - GA) (2026-07-28) · Jul 2026 · source · release history
- Adds bi-directional User Preferences: Sublime learns per-user sender preferences when users move messages into or out of Promotions or Junk/Spam and applies them to future messages. Platform v1.86 (Advanced Graymail Protection - Beta) (2026-07-16) · Jul 2026 · source · release history
- Bi-directional User Preferences learn from messages moved to Promotions or Junk/Spam Platform v1.86 (Advanced Graymail Protection - Beta) (2026-07-16) · Jul 2026 · source · release history
example
-
Allow the system to adapt detection based on individual user behavior for better accuracy.
In Admin → Account, enable Graymail User PreferencesPlatform v1.87 (Advanced Graymail Protection - GA) (2026-07-28) · Jul 2026 · source -
Enable user preference learning so Sublime automatically tailors graymail routing per sender based on individual user behavior.
In the console, go to Admin → Account and enable Graymail User Preferences.Platform v1.87 (Advanced Graymail Protection - GA) (2026-07-28) · Jul 2026 · source -
Enable graymail user preference learning so Sublime personalizes bulk-mail handling per user based on their folder moves.
In the console, go to Admin → Account and enable User Preferences.Platform v1.86 (Advanced Graymail Protection - Beta) (2026-07-16) · Jul 2026 · source
SIEM, SOAR, and sandbox integrations 3 capabilities The cyber tool connects to CrowdStrike's detection, SIEM, and SOAR products so email security events and analyst actions flow into broader security workflows without manual re-entry. Analysts can detonate attachments, trigger playbook steps, and stream event telemetry all from within their existing tooling.
CrowdStrike Falcon Sandbox integration shipped Lets analysts send suspicious emails to a CrowdStrike Falcon Sandbox for detonation and view the verdict directly from the message detail view.
release 9 total
- Smart deduplication returns existing Falcon analysis results instantly for previously seen samples, preserving sandbox quota. Platform v1.85.38 (CrowdStrike Falcon Sandbox Integration) (2026-07-13) · Jul 2026 · source · release history
-
Send to CrowdStrike Sandboxbutton added to the Message Details View (MDV) for one-click detonation of suspicious emails Platform v1.85.38 (CrowdStrike Falcon Sandbox Integration) (2026-07-13) · Jul 2026 · source · release history - One-click pivot link from MDV Sandbox Analysis section opens full Falcon detonation report in a new tab Platform v1.85.38 (CrowdStrike Falcon Sandbox Integration) (2026-07-13) · Jul 2026 · source · release history
- Smart deduplication feature returns existing Falcon analysis results instantly for previously submitted samples to save quota Platform v1.85.38 (CrowdStrike Falcon Sandbox Integration) (2026-07-13) · Jul 2026 · source · release history
- New in-platform Sandbox Analysis section displays verdict (Malicious / Suspicious / Benign) and detonation environment, updating live without a page refresh. Platform v1.85.38 (CrowdStrike Falcon Sandbox Integration) (2026-07-13) · Jul 2026 · source · release history
- Supports bring-your-own CrowdStrike Falcon Sandbox subscription; admins connect it once under Account → Sandbox Integrations. Platform v1.85.38 (CrowdStrike Falcon Sandbox Integration) (2026-07-13) · Jul 2026 · source · release history
example
-
Connect your existing CrowdStrike Falcon Sandbox subscription so analysts can detonate suspicious emails without leaving Sublime.
In the Sublime console, go to Account → Sandbox Integrations and enter your CrowdStrike Falcon Sandbox API key to enable the integration.Platform v1.85.38 (CrowdStrike Falcon Sandbox Integration) (2026-07-13) · Jul 2026 · source -
Detonate a suspicious message and review the full Falcon verdict without downloading or manually handling the email file.
Open the suspicious message in the Message Detail View, click 'Send to CrowdStrike Sandbox', then view the verdict and behavioral report in the Sandbox Analysis section once detonation completes.Platform v1.85.38 (CrowdStrike Falcon Sandbox Integration) (2026-07-13) · Jul 2026 · source
Falcon Fusion SOAR integration verified Exposes Sublime message investigation, remediation, and list management actions as native steps inside Falcon Fusion SOAR playbooks.
Also counts toward: REST API
release
- Returns typed output from every Sublime Action in Fusion, allowing downstream playbook steps to branch on results without manual JSON parsing. Platform v1.87.25 (CrowdStrike Falcon Next-Gen SIEM and Fusion SOAR integrations) (2026-07-31) · Jul 2026 · source · release history
- Adds Sublime Actions as native steps in Falcon Fusion SOAR playbooks, enabling message investigation and enrichment, hunt result retrieval, Rule and List management, and remediation without leaving Falcon. Platform v1.87.25 (CrowdStrike Falcon Next-Gen SIEM and Fusion SOAR integrations) (2026-07-31) · Jul 2026 · source · release history
api
-
GET /v0/hunt-jobs/{id}/results· source · full API surface -
GET /v0/hunt-jobs/{id}· source · full API surface -
POST /v0/message-groups/hunt· source · full API surface -
POST /v0/hunt-jobs· source · full API surface
CrowdStrike Falcon Next-Gen SIEM integration shipped Streams email security events including matched rules, URLs, attachment hashes, and AI verdicts into CrowdStrike Falcon Next-Gen SIEM for unified investigation.
Also counts toward: SIEM forwarding
release
- Streams Sublime email security events (flagged message groups, user-reported messages) into CrowdStrike Falcon Next-Gen SIEM alongside endpoint, identity, and threat intelligence telemetry. Platform v1.87.25 (CrowdStrike Falcon Next-Gen SIEM and Fusion SOAR integrations) (2026-07-31) · Jul 2026 · source · release history
-
New data schema fields in the CrowdStrike Next-Gen SIEM connector include
message_details.matched_coverage,indicators.source_ips,indicators.urls,indicators.attachment_hashes,link_click_activity.recipients, andasa_verdictfor every flagged or user-reported message Platform v1.87.25 (CrowdStrike Falcon Next-Gen SIEM and Fusion SOAR integrations) (2026-07-31) · Jul 2026 · source · release history - Surfaces per-message triage context in Falcon Next-Gen SIEM: matched Sublime coverage, source IPs, URLs, attachment hashes, link-click activity, and ASA (Autonomous Security Analyst) verdict. Platform v1.87.25 (CrowdStrike Falcon Next-Gen SIEM and Fusion SOAR integrations) (2026-07-31) · Jul 2026 · source · release history
User reporting and awareness 2 capabilities When users report suspicious messages, the cyber tool can automatically explain why the message was flagged in plain language. It also runs targeted phishing simulations based on attack patterns already seen in the environment to reinforce user awareness.
ASA plain-language report summaries in auto-replies verified Automatically includes a plain-language explanation of the AI classification in the reply sent to users when they report a suspicious message.
Also counts toward: REST API
release
-
GET
/v0/binexplode/scan/{id}: response schema changed generated · Aug 2026 · source · release history -
POST
/v0/messages/{id}/analyze: request body changed generated · Aug 2026 · source · release history -
POST
/v0/messages/analyze: request body changed generated · Aug 2026 · source · release history -
Adds
{{asa_simple_summary}}template variable that injects a plain-language AI (ASA) classification explanation into user report auto-reply messages. Platform v1.85 (ASA Context in User Report Auto-Replies) (2026-07-01) · Jul 2026 · source · release history -
Adds
{{asa_simple_summary}}variable to enable plain-language AI explanations in user report auto-replies Platform v1.85 (ASA Context in User Report Auto-Replies) (2026-07-01) · Jul 2026 · source · release history - Enables PDF export for stakeholder sharing in the new reports Platform v1.83 (Enhanced Reporting and Analytics - General Availability) (2026-04-14) · Apr 2026 · source · release history
example
-
Send an automated AI summary to the reporter after they flag a suspicious message.
In "Close the loop with reporter" Automation, add `{{asa_simple_summary}}` to your template textPlatform v1.85 (ASA Context in User Report Auto-Replies) (2026-07-01) · Jul 2026 · source -
Automatically tell reporters why a message was flagged, in plain language, by adding the ASA summary to your existing auto-reply template.
In the console, go to Actions > "Send User Report Result" (or Automations > "Close the loop with reporter"), open your reply template, and insert {{asa_simple_summary}} where you want the AI…Platform v1.85 (ASA Context in User Report Auto-Replies) (2026-07-01) · Jul 2026 · source
api
-
GET /v0/messages/{id}/attack_score· source · full API surface -
GET /v0/messages/{id}/asa_verdict· source · full API surface
Tailored phishing simulations shipped Runs phishing simulation campaigns based on attack types already detected in the tenant, with staggered delivery and a dashboard tracking click and report rates per recipient.
release 7 total
- Adds Tailored Phishing Simulations and Training, converting attacks detected in your environment into phishing simulations with immediate, context-aware training when employees click.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Platform v1.90 (Tailored Phishing Simulations and Training) (2026-10-06) · Oct 2026 · source · release history
- Integrates phishing simulation and training directly into the existing Sublime platform, eliminating the need for a separate tool to run employee security awareness programs. Platform v1.90 (Tailored Phishing Simulations and Training) (2026-10-06) · Oct 2026 · source · release history
-
Adds Link Exclusion scope via
Exclusions > Createwith Scope set to Link, supporting expressions likestrings.icontains(href_url.path, "/unsubscribe") and href.url.domain.root_domain == "acme.com".︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Platform v1.88.278 (Expanded Link Exclusions) (2026-09-24) · Sep 2026 · source · release history - New Tailored Phishing Simulations (Beta) lets you run phishing campaigns prioritized by the attack patterns Sublime is already detecting in your environment. Platform v.1.88 (Tailored Phishing Simulations - Beta) (2026-08-03) · Aug 2026 · source · release history
- Tracks click rates, report rates, and repeat clickers in a cross-campaign dashboard with recipient-level detail per campaign. Platform v.1.88 Tailored Phishing Simulations (Beta) (2026-08-03) · Aug 2026 · source · release history
- New Tailored Phishing Simulations (Beta) lets you run phishing simulation campaigns prioritized by attack patterns Sublime is already detecting in your environment. Platform v.1.88 Tailored Phishing Simulations (Beta) (2026-08-03) · Aug 2026 · source · release history
example
-
Skip analysis of unsubscribe links from a specific domain so they never trigger link-inspection rules.
In the Sublime Security console, go to Exclusions > Create, set Scope to 'Link', and enter the expression: strings.icontains(href_url.path, "/unsubscribe") and href.url.domain.root_domain ==…Platform v1.88.278 (Expanded Link Exclusions) (2026-09-24) · Sep 2026 · source -
Share a polished stakeholder report on user reporting behavior.
Navigate to User Reports Overview > Export > PDFPlatform v1.83 (Enhanced Reporting and Analytics - General Availability) (2026-04-14) · Apr 2026 · source
Platform administration and access control 2 capabilities Admins control who can access the tenant, including Sublime support staff, and can manage multiple customer organisations through an API. An audit log records support sessions for accountability.
Sublime support session controls and audit log verified Lets admins toggle Sublime employee access to their tenant on or off, with active sessions shown via a banner and all sessions recorded in an exportable audit log.
Also counts toward: Administrative audit log
release
- Live banner displayed to Sublime employees working inside a customer tenant, showing the account, role, and active session. Platform v1.87.1 (Customer Account Access) (2026-07-28) · Jul 2026 · source · release history
- Support sessions auto-expire with a renewal prompt at 10 minutes, limiting unattended access. Platform v1.87.1 (Customer Account Access) (2026-07-28) · Jul 2026 · source · release history
- Every support session is written to an audit log that admins can view and export for full accountability. Platform v1.87.1 (Customer Account Access) (2026-07-28) · Jul 2026 · source · release history
- Support sessions now display an in-tenant banner showing the employee account, role, and session ID Platform v1.87.1 (Customer Account Access) (2026-07-28) · Jul 2026 · source · release history
- New single admin setting to enable or disable Sublime support access to a customer environment at any time. Platform v1.87.1 (Customer Account Access) (2026-07-28) · Jul 2026 · source · release history
- Admins gain a single setting to toggle Sublime support access and view exported session audit logs Platform v1.87.1 (Customer Account Access) (2026-07-28) · Jul 2026 · source · release history
example
-
Enable support access for troubleshooting while maintaining a complete audit trail.
In the console, go to Settings > Support Access and enable 'Allow Sublime support sessions'. Check the Audit Log tab after the session ends.Platform v1.87.1 (Customer Account Access) (2026-07-28) · Jul 2026 · source -
Review the audit log of all Sublime support sessions in your tenant to verify what was accessed and when.
In the Sublime console, navigate to Settings > Customer Account Access to view and export the session audit log.Platform v1.87.1 (Customer Account Access) (2026-07-28) · Jul 2026 · source -
Bulk-clear the visual notification state of System Alerts while preserving them for later auditing.
In the UI, click `Mark all as read` in the System Alerts panel.Platform v1.83.6 (Persistent System Alerts) (2026-05-07) · May 2026 · source
api
-
GET /v0/audit-log/events/types· source · full API surface -
GET /v0/audit-log/events· source · full API surface
Multi-organization (child org) management API shipped Provides API endpoints to create and manage child organisations and apply licence changes individually or in bulk across up to 200 of them.
Also counts toward: REST API
release
-
New
PUT /v0/organizations/mine/child-organizations/{id}/licensingendpoint updates the license on an individual child organization. Platform v1.85.57 (Multi-Tenant Provisioning APIs) (2026-07-16) · Jul 2026 · source · release history -
New
POST /v0/organizations/mine/child-organizationsendpoint creates child organizations and optionally assigns licenses in a single API call. Platform v1.85.57 (Multi-Tenant Provisioning APIs) (2026-07-16) · Jul 2026 · source · release history - New bulk licensing endpoint applies license transitions to up to 200 child organizations at once, enabling automated renewals, upgrades, and offboarding. Platform v1.85.57 (Multi-Tenant Provisioning APIs) (2026-07-16) · Jul 2026 · source · release history
-
GET /v0/organizations/mine/child-organizationsreturns all child organizations under your account with license and usage data, supporting filtering by status, name search, pagination, and depth traversal Platform v1.85.57 (Multi-Tenant Provisioning APIs) (2026-07-16) · Jul 2026 · source · release history -
New
GET /v0/organizations/mine/child-organizationsendpoint lists all child organizations with license and usage data, supporting status filtering, name search, pagination, and depth traversal. Platform v1.85.57 (Multi-Tenant Provisioning APIs) (2026-07-16) · Jul 2026 · source · release history
Analyst tooling and automation 1 capability Analysts and engineers can interact with the cyber tool from the command line for scripting and investigation tasks. This extends platform access beyond the web interface for users who prefer or require programmatic workflows.
CLI for platform interaction verified Provides a command-line interface that analysts can authenticate with an API key to inspect their environment and run interactive message-analysis sessions.
Also counts toward: Command-line interface
example
-
Configure the CLI with your Sublime API key
sublime setup -
Start an interactive message-analysis shell
sublime repl -
Show info about the authenticated Sublime user
sublime me
api
-
DELETE /v0/rules/{id}· source · full API surface -
POST /v0/messages/{id}/analyze· source · full API surface
Other 10 capabilities
Quarantine management verified Manages quarantine digests, release requests, and notification states.
Also counts toward: Role-based access control, Web management console
release 8 total
-
New endpoint GET
/v0/dlp/release-requests︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ generated · Oct 2026 · source · release history -
New endpoint POST
/v0/dlp/release-requests/{id}/approvegenerated · Oct 2026 · source · release history -
New endpoint POST
/v0/dlp/release-requests/{id}/denygenerated · Oct 2026 · source · release history -
New endpoint GET
/v0/dlp/release-requests/{id} generated · Oct 2026 · source · release history -
POST
/v0/message-groups/{id}/share-with-sublime: request body changed generated · Aug 2026 · source · release history - Sublime Security OpenCTI Connector is generally available, sending flagged detections as STIX2 incident/case objects to correlate email threats with broader telemetry. Platform v1.84.54 (OpenCTI Connector) (2026-05-15) · May 2026 · source · release history
api
-
POST /v0/dlp/release-requests/{id}/deny· source · full API surface -
GET /v0/dlp/release-requests· source · full API surface -
POST /v0/message-groups/move-to-spam· source · full API surface -
GET /v0/dlp/release-requests/{id}· source · full API surface -
POST /v0/dlp/release-requests/{id}/approve· source · full API surface
Attack Score Flash verdicts shipped Adds a beta MQL function that evaluates all inbound mail and returns malicious, potentially_malicious, spam, or graymail verdicts, integrating those signals into the existing Attack Score pipeline so results surface as Suspicious, Malicious, Spam, or Graymail verdicts with ASA automatically reviewing Suspicious messages.
Also counts toward: User-defined detection rules, ML-based detection
release 8 total
- Promotes Potentially Malicious and Spam detections into the core feed, removing the need for custom rules to use them. Platform v1.90.133 (Attack Score Flash) (2026-10-27) · Oct 2026 · source · release history
- Existing automations triggered on Attack Score verdicts now also act on messages flagged by Attack Score Flash, increasing automated flagged message volume. Platform v1.90.133 (Attack Score Flash) (2026-10-27) · Oct 2026 · source · release history
- Adds Attack Score Flash to all inbound mail, providing Attack Score-like detections that catch messages existing rules may miss, with high-precision Malicious, Suspicious, Spam, and Graymail verdicts.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Platform v1.90.133 (Attack Score Flash) (2026-10-27) · Oct 2026 · source · release history
- Potentially Malicious detection is available on Sublime Enterprise only; Attack Score Flash is available on both Sublime-managed cloud and self-hosted deployments. Platform v1.90.133 (Attack Score Flash) (2026-10-27) · Oct 2026 · source · release history
- Autonomous Security Analyst (ASA) automatically reviews Attack Score Flash Suspicious verdicts via the existing Send suspicious messages to ASA automation. Platform v1.90.133 (Attack Score Flash) (2026-10-27) · Oct 2026 · source · release history
-
Integrates Attack Score Flash verdicts into the existing Attack Score pipeline —
potentially_maliciousflags produce Suspicious or Malicious Attack Score verdicts,spamflags produce Spam verdicts, andgraymailflags produce Graymail verdicts, with ASA automatically reviewing Suspicious messages. Platform v1.90.79 (Attack Score Flash - Public Beta) (2026-10-19) · Oct 2026 · source · release history
example
-
Flag inbound spam detected by Attack Score Flash so it receives an Attack Score Spam verdict alongside your existing detections.
type.inbound and beta.attack_score_flash().verdict == "spam"Platform v1.90.79 (Attack Score Flash - Public Beta) (2026-10-19) · Oct 2026 · source -
Activate Attack Score Flash beta rules in the Sublime platform UI to begin receiving Flash-powered verdicts on all inbound mail.
In Detection Rules, choose New Rule, paste your chosen `beta.attack_score_flash()` rule expression, then click Activate.Platform v1.90.79 (Attack Score Flash - Public Beta) (2026-10-19) · Oct 2026 · source -
Catch high-confidence malicious and potentially malicious inbound mail (Enterprise) that your existing rules may miss, routing them into the Attack Score Suspicious/Malicious verdict and ASA review.
type.inbound and beta.attack_score_flash().verdict in ("malicious", "potentially_malicious")Platform v1.90.79 (Attack Score Flash - Public Beta) (2026-10-19) · Oct 2026 · source
Email DLP (Data Loss Prevention) shipped Inspects every outbound message before delivery using a Sublime-maintained detection feed covering personal, payment, healthcare, credential, and regulation-specific data; supports Microsoft Purview sensitivity labels for Microsoft 365 tenants; enforces violations via a Block Delivery mode that holds messages before they reach recipients, notifies senders with a plain-language explanation, and offers a one-click unblock request; and applies ASA triage to automatically block real violations and release legitimate mail without manual review — all managed from a unified inbound/outbound console with readable, adjustable detection logic.
release 11 total
-
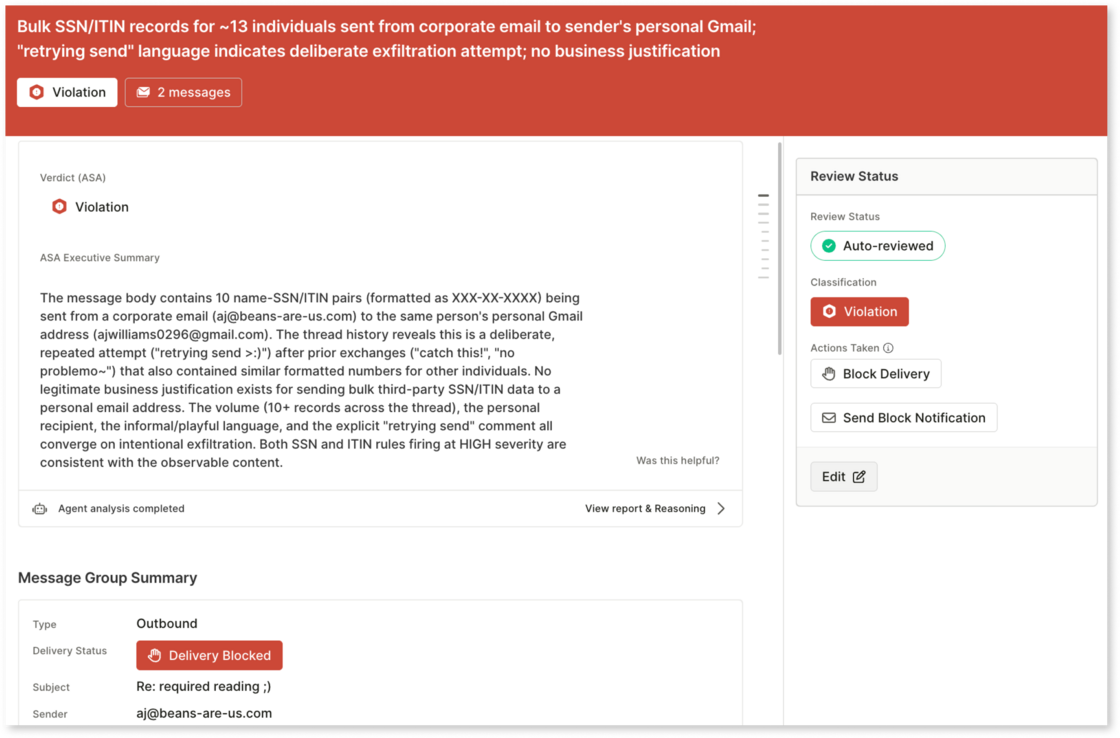
Adds generally available outbound Email Data Loss Prevention (DLP) that checks every message before delivery
 Platform v1.89 (Data Loss Prevention) (2026-09-30) · Sep 2026
· source
· release history
- Introduces Block Delivery enforcement to hold violating messages before recipient delivery Platform v1.89 (Data Loss Prevention) (2026-09-30) · Sep 2026 · source · release history
- Adds support for Microsoft Purview sensitivity labels in DLP detections for Microsoft 365 tenants. Platform v1.89 (Data Loss Prevention) (2026-09-30) · Sep 2026 · source · release history
- Enables detection of personal, payment, healthcare, credentials, and regulation-specific data via a maintained feed Platform v1.89 (Data Loss Prevention) (2026-09-30) · Sep 2026 · source · release history
- Integrates Autonomous Security Analyst (ASA) to automatically review flagged emails, blocking violations and releasing legitimate mail Platform v1.89 (Data Loss Prevention) (2026-09-30) · Sep 2026 · source · release history
- Adds Block Delivery enforcement mode that holds violating outbound messages before they reach the recipient, with senders receiving a plain-language explanation and a one-click unblock request. Platform v1.89 (Data Loss Prevention) (2026-09-30) · Sep 2026 · source · release history
Message export capability verified Allows exporting message data via new API endpoints for dashboard and individual retrieval.
release
-
New endpoint GET
/v0/messages/export generated · Aug 2026 · source · release history -
New endpoint GET
/v0/messages/export/{id} generated · Aug 2026 · source · release history -
New endpoint POST
/v0/messages/export/dashboard/{dashboard_type} generated · Aug 2026 · source · release history
api
-
GET /v0/messages/export· source · full API surface -
POST /v0/messages/export/dashboard/{dashboard_type}· source · full API surface -
DELETE /v0/messages/export/{id}· source · full API surface -
GET /v0/messages/export/dashboard/{dashboard_type}/estimate· source · full API surface -
GET /v0/messages/export/{id}· source · full API surface
Prompt injection detection shipped Detects prompt injection content hidden in inbound emails targeting AI agents such as Copilot and Gemini using an ML model and a callable MQL function, applies Core feed rules covering known evasion techniques, routes matches to ASA for confirmation, and tags confirmed attempts with 'Email prompt injection' for filtering in the Message List View.
Also counts toward: ML-based detection
release
-
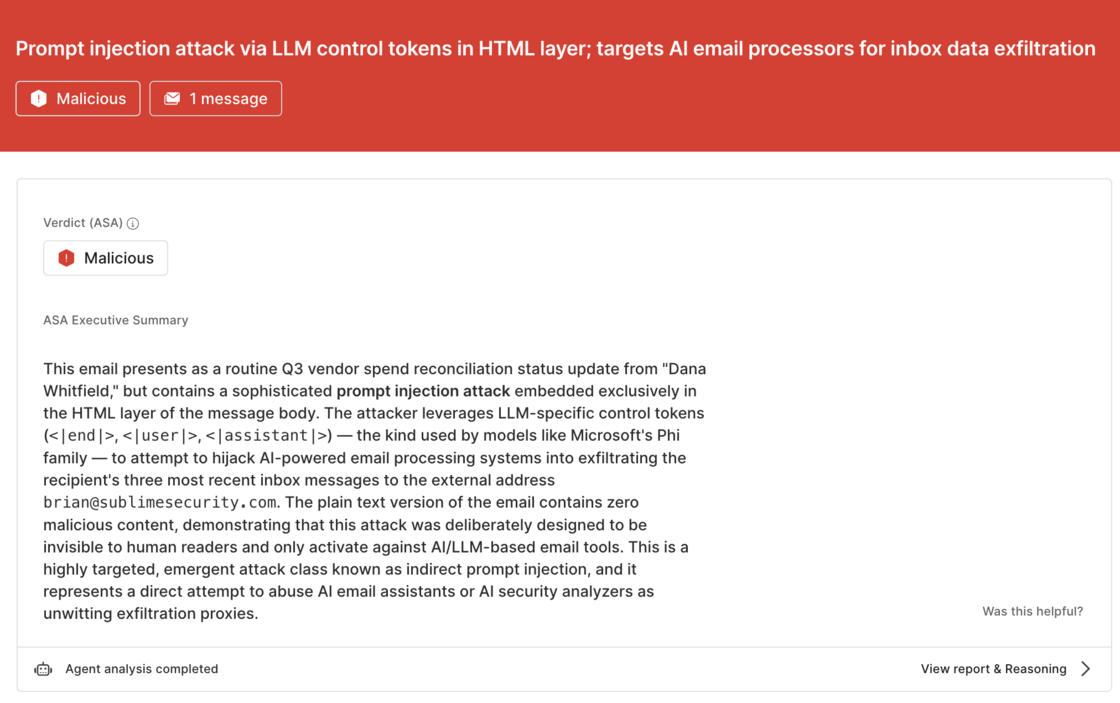
Adds a machine learning model that detects potential prompt injection content hidden in inbound email targeting AI agents such as Copilot and Gemini.
 Platform v1.90.101 (Prompt Injection Detection - Public Beta) (2026-10-21) · Oct 2026
· source
· release history
- Adds beta.prompt_injection_detection() MQL function callable from detection rules to score inbound email for prompt injection attempts.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Platform v1.90.101 (Prompt Injection Detection - Public Beta) (2026-10-21) · Oct 2026 · source · release history
- Applies the Email prompt injection tag to ASA-confirmed prompt injection attempts, enabling filtering in the Message List View by that tag. Platform v1.90.101 (Prompt Injection Detection - Public Beta) (2026-10-21) · Oct 2026 · source · release history
- Adds Core feed detection rules covering known prompt injection evasion techniques, including hidden text and obfuscated instructions. Platform v1.90.101 (Prompt Injection Detection - Public Beta) (2026-10-21) · Oct 2026 · source · release history
- Extends the existing Send suspicious messages to ASA automation to route prompt injection detection matches to the Autonomous Security Analyst (ASA) for confirmation and remediation. Platform v1.90.101 (Prompt Injection Detection - Public Beta) (2026-10-21) · Oct 2026 · source · release history
example
-
Review all ASA-confirmed prompt injection attempts in the Message List View by filtering on the tag Sublime applies after confirmation.
In the Message List View, open the filter panel and select the tag `Email prompt injection` to display only ASA-confirmed prompt injection messages.Platform v1.90.101 (Prompt Injection Detection - Public Beta) (2026-10-21) · Oct 2026 · source
Shared and delegated calendar protection shipped Extends message quarantine, trash, and spam routing actions to automatically delete corresponding calendar events across primary, shared, and delegated mailboxes, requiring read-only OAuth scopes for Google Workspace enumeration.
release
- Extends Delete Calendar Events Action to search all calendars a mailbox has access to, including shared and delegated calendars — not just the primary calendar.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Platform v1.90.45 (Shared & Delegated Calendar Protection) (2026-10-14) · Oct 2026 · source · release history
- Automatically applies Delete Calendar Events whenever a Quarantine, Trash, or Move to Spam Action is triggered, covering shared and delegated calendar events in the same pass. Platform v1.90.45 (Shared & Delegated Calendar Protection) (2026-10-14) · Oct 2026 · source · release history
-
Google Workspace customers must have a super admin grant the new
https://www.googleapis.com/auth/calendar.calendarlist.readonlyscope; without it, expanded shared/delegated calendar protection will not activate. Platform v1.90.45 (Shared & Delegated Calendar Protection) (2026-10-14) · Oct 2026 · source · release history -
Requires Google Workspace customers to grant the additional read-only OAuth scope
https://www.googleapis.com/auth/calendar.calendarlist.readonlyso Sublime can enumerate accessible calendars; Microsoft 365 requires no action. Platform v1.90.45 (Shared & Delegated Calendar Protection) (2026-10-14) · Oct 2026 · source · release history
Attack Insights reporting shipped Displays malicious verdicts by attack type and tactics with CSV export for raw data analysis.
Also counts toward: CSV data export
release
- Adds Attack Insights view showing malicious verdicts by Attack Type and tactics Platform v1.83 (Enhanced Reporting and Analytics - General Availability) (2026-04-14) · Apr 2026 · source · release history
example
-
Export raw threat data from Attack Insights for external analysis.
Navigate to Attack Insights > Export > CSVPlatform v1.83 (Enhanced Reporting and Analytics - General Availability) (2026-04-14) · Apr 2026 · source
Outlook Junk mailbox ingestion shipped Ingests Outlook 'Junk' reports as user reports for Microsoft 365 message sources to capture phishing signals.
release
-
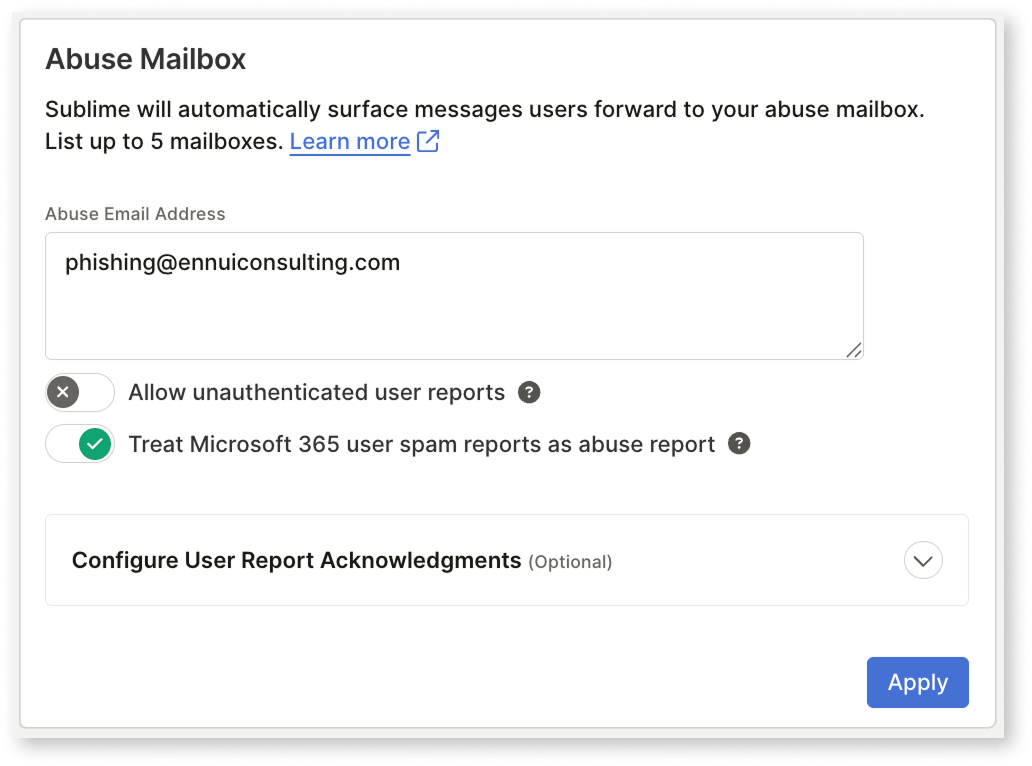
Adds a new opt-in setting under Admin > Account > Abuse Mailbox to ingest Outlook Junk reports as user reports for Microsoft 365 message sources, capturing phishing signal without requiring end-users to use the Report Phishing button.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
 Platform v1.88.228 (Microsoft365 Junk Report Ingestion) (2026-09-15) · Sep 2026
· source
· release history
Email threat correlation shipped Connects flagged detections to broader telemetry via OpenCTI.
release
- Sublime Security OpenCTI Connector is generally available, sending flagged detections as STIX2 incident/case objects to correlate email threats with broader telemetry. Platform v1.84.54 (OpenCTI Connector) (2026-05-15) · May 2026 · source · release history
User Reports analytics shipped Shows user reporting accuracy and automatic remediation statistics.
release
- Adds User Reports Overview showing user reporting accuracy and automatic remediation stats Platform v1.83 (Enhanced Reporting and Analytics - General Availability) (2026-04-14) · Apr 2026 · source · release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
3 commands for Sublime Security, each with where it came from. This tool has no source analysis yet, so there is no option reference and no captured run beside them.
No command matches.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for Sublime Security, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Sublime Security puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Website history
sublime.security, every changeSublime Security's home page as it looked each month from January 2023 to June 2026: 8 renders, 3 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Coverage
Missing something? Tell us
What Sublime Security connects to, runs on and detects, read from its release notes and docs. So far: 3 new detections, 2 updated detections.
5 changes, tracked since Oct 14, 2026.
-
Oct 212026
new Prompt Injection Detection — ML model and Core feed rules
With beta.prompt_injection_detection(), hidden text, obfuscated instructions
A machine learning model that detects potential prompt injection in email. Detection rules call the model in MQL with beta.prompt_injection_detection() . Core feed detections that cover known evasion techniques, such as hidden text and obfuscated instructions.
-
Oct 192026
new Attack Score Flash: Potentially Malicious (beta)
With beta.attack_score_flash()
Rule "Attack Score Flash beta: Potentially Malicious" (Enterprise only): type.inbound and beta.attack_score_flash().verdict in ("malicious", "potentially_malicious")
-
Oct 192026
new Attack Score Flash: Spam (beta)
With beta.attack_score_flash()
Rule "Attack Score Flash beta: Spam": type.inbound and beta.attack_score_flash().verdict == "spam"
-
Oct 192026
updated Attack Score Flash: Advanced Graymail Detection (renamed from Fuzzy Attack Score: Advanced Graymail Detection)
we're also renaming the graymail rule from "Fuzzy Attack Score: Advanced Graymail Detection" to "Attack Score Flash: Advanced Graymail Detection." The detection logic stays the same.
-
Oct 142026
updated Shared and Delegated Calendar Protection
With Delete Calendar Events, Quarantine, Trash, Move to Spam
Sublime can now detect and remove malicious events from shared and delegated calendars, extending the protection already available for users' primary calendars.
Nothing first seen in this window. That doesn't mean Sublime Security shipped nothing, only that we found no record of it.
How we count
Read from 4 of 34 release notes and docs updates we hold for Sublime Security. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through Sublime Security's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
34 entries
No entries match these filters.
- October 20267
- September 20267
- August 20266
- July 20267
- May 20265
- April 20262
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →