Introducing the AI Agent Kill Switch: Instant Single-User Revocation (2026-10-29)commercial
The section your link pointed to isn't on Aembit's page any more, so we've brought you to the top.
Aembit is a non-human identitynon-human identityA non-human identity, an account or credential used by software or a device rather than a person. Service accounts, workload identities and automation tokens need their own permissions and lifecycle controls. and access management platform that verifies workload and AI agent identities, evaluates policy, and issues short-lived credentials.
Aembit is a commercial identity-access platform that issues short-lived credentials to workloads and AI agents instead of relying on static secrets, run as a cloud control plane paired with components deployed into the customer's environment — an Agent Proxy or Edge Component on Kubernetes, VMs, or serverless, plus Edge SDKs for TypeScript and Python when a workload should attest and fetch credentials in-process. It is aimed at platform and security teams managing non-human identity across cloud providers and AI services, covering workload identityworkload identityAn identity assigned to software, such as a service or container, rather than a person. It lets the workload authenticate and receive permissions without sharing a user's credentials. federation to AWS, Azure, GCP, Anthropic Claude, and OpenAI, and an MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Identity Gateway that governs tool traffic agents send to MCP servers, including a CrowdStrike AIDR integration for inspecting that traffic. Launched in 2021, it ships frequently, with 25 tracked releases and the latest only 12 days old.
Aembit is a non-human identity and access management platform that verifies workload and AI agent identities, evaluates policy, and issues short-lived credentials.
Which of my workloads are still using static API keys instead of short-lived credentials?
checks whether a workload's credential provider is a Workload Identity Federation type (AWS STS, Azure Entra, GCP, Anthropic Claude, OpenAI) versus a stored static key, so you can see which connections still depend on secrets that can leak
Which policy let this AI agent reach this MCP server, and what happened when it got there?
ties the request to the ordered chain of authorization and credential events behind it, plus the allow, block, or transform verdict recorded against the agent's identity, the target server, and the policy
Can this agent's traffic to a sensitive tool be inspected before it goes through?
lets you attach a content-security check to that one Access Policy so tool listings, inputs, and outputs are evaluated inline, while every other policy keeps running unchanged
What should happen to a request if the content-inspection service is unreachable?
is set per policy as fail-open or fail-closed, with every such failure written to the workload event log
Who or what actually called this Server Workload, and did the response ever get an outcome?
records severity, result, and reason on the response event itself, so a request's outcome is no longer lost between the request and the reply
Which credential path is my workload actually using to reach Aembit?
compares Agent Proxy, Edge SDK, Aembit CLI, and Edge API side by side so you can tell which mechanism a given service, container, or pipeline is retrieving credentials through
Built from Aembit's releases, docs, README and our own runs.
“Seen” marks the month we first spotted a release the vendor didn't date.
Group names and tags are our labels.
+Access policy and credential delivery modelshippedAembit operates a split management and control plane where administrators define access policies and credential providers, and workloads retrieve credentials at runtime through an Agent Proxy, Edge SDK, CLI, or Edge API.65 releases · 17 other sources · first seen Oct 2023▸
Also counts toward: Agent-based deployment, Command-line interface, Client SDKs
release
65 total
MCP Identity Gateway now applies a new credential on the user's very next request after an MCP User-Based Access Token Credential Provider authorization, instead of returning errors until the cached credential expired.
changelog · Oct 2026
· source
· release history
Extends MCP Server Workloads to support any authentication method available to HTTP Server Workloads, including API Key, HTTP Authentication with the Basic scheme, and Static HTTP Headers.
changelog · Oct 2026
· source
· release history
Adds Header authentication scheme support to MCP Identity Gateway, sending credentials to MCP servers in a named header so MCP servers that accept an API key via a custom header now receive it correctly.
changelog · Oct 2026
· source
· release history
Extends centralized access policy management to cover Meta Muse alongside Microsoft Copilot Studio, Claude, ChatGPT, Gemini, and custom LLM-based agents under a single policy model.
Aembit Launches Identity and Access Security Controls for Meta Muse (2026-10-05) · Oct 2026
· source
· release history
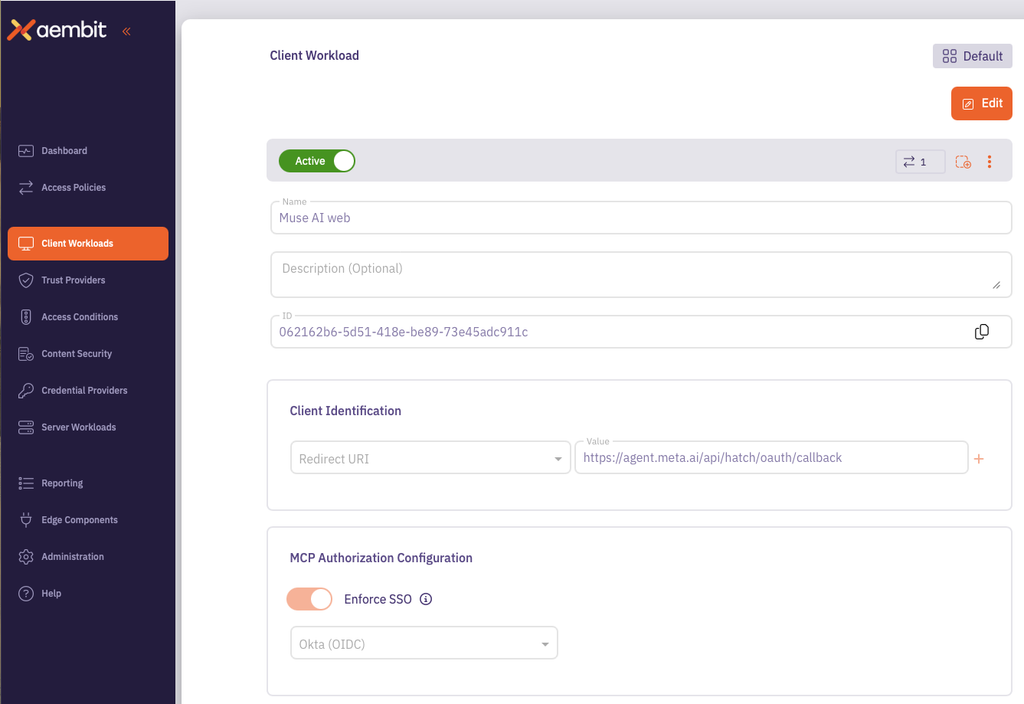
Adds Meta Muse as a supported client workload in Aembit's IAM for Agentic AI Platform, routing Muse's enterprise resource requests through the MCP Identity Gateway and MCP Authorization Server for policy-evaluated, short-lived credential issuance.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Aembit Launches Identity and Access Security Controls for Meta Muse (2026-10-05) · Oct 2026
· source
· release history
Introduces MCP Authorization Server as the policy decision point that issues short-lived, scoped credentials to authorized Meta Muse workloads.
Aembit Launches Identity and Access Security Controls for Meta Muse (2026-10-05) · Oct 2026
· source
· release history
docs
15 total
Access control Section titled âAccess controlâ The practice of regulating access to resources or systems based on permissions and authorization policies.
seen Oct 2026
· source
Server Workloads can be virtually any service that provides functionality to other systems. They range from modern cloud-native APIs and microservices to legacy on-premises databases. They also include third-party SaaS platforms like Snowflake and Stripe, and AI services like OpenAI and Claude.
seen Oct 2026
· source
Select Existing tab in the Access Policy builder now searches and pages through all the entities you can access. Lists of more than 100 Client Workloads, Server Workloads, Trust Providers, Credential Providers, or Access Conditions no longer hide entries past the first page.
docs update · Oct 2026
· source
Agent Proxy 1.34.6014 injects credentials for Server Workloads whose Application Protocol Agent Proxy handles this traffic as HTTP and injects the credential the same way it does for HTTP Server Workloads. Earlier versions passed MCP traffic through without injecting a credential.
docs update · Oct 2026
· source
When Aembit creates a user through single sign-on, it now reads the userâs first and last names from standard OpenID Connect (OIDC) profile claims, including given_name family_name If a first or last name claim is missing, Aembit takes that name from the name claim.
docs update · Sep 2026
· source
The Aembit GitHub Action can now choose which AWS Security Token Service (STS) Federation Credential Provider to use when an Access Policy holds more than one. An Access Policy can hold more than one AWS STS Federation Credential Provider, each with its own Access Key ID selector.
docs update · Sep 2026
· source
example
Configure the Muse skill file so the agent can list and invoke tools through the Aembit MCP Identity Gateway using short-lived credentials.$ CREDENTIAL_NAME = "custom.aembit-mcp-gateway" MCP_URL = "https://<tenant>.mcpgateway.aembit.io/mcp" ALLOWED_HOSTS = ["<tenant>.mcpgateway.aembit.io", "<tenant>.id.useast2.aembit.io"]
Aembit Launches Identity and Access Security Controls for Meta Muse (2026-10-05) · Oct 2026
· source
Let a GitHub-hosted Actions runner assume a specific IAM role from an Access Policy that holds multiple AWS STS Federation Credential Providers, identified by Access Key ID selector.$ - uses: aembit/aembit-github-action@v1 with: aws-access-key-id: AKIA<SELECTOR_FOR_TARGET_ROLE>
changelog · Sep 2026
· source
+Workload event logging and audit trailshippedRecords detailed workload events — including authorization chains, severity, outcome fields, and failure reasons — so operators can trace every access request back to its policy, credential retrieval, and identity context.26 releases · 3 other sources · first seen Nov 2023▸
release
26 total
Workload events now record credential injection as failed when MCP Identity Gateway cannot add a credential to a request as a header or query parameter.
changelog · Oct 2026
· source
· release history
Agent Controller authentication errors now name the Agent Controller ID that failed, prompting you to confirm it is valid and active in your Aembit Tenant.
changelog · Oct 2026
· source
· release history
Adds per-MCP-server workload events for tools/list and resources/list fan-out requests in MCP Identity Gateway, including events for servers that fail or are skipped because they do not support the method, naming the Server Workload and recording the server's host and HTTP status when known.
changelog · Oct 2026
· source
· release history
Adds access.registration event type to Access Authorization Events, recording each Dynamic Client Registration (DCR) request an MCP client sends — successful registrations log client ID, client name, redirect URIs, grant types, and response types at severity Info; failed registrations log at severity Error with…
changelog · Oct 2026
· source
· release history
Centralizes audit logging for every agent access decision, capturing which agent acted, on whose behalf, what it touched, and which policy permitted the request.
Personal AI Agents Are Here, and Aembit Customers Can Secure Them Today (2026-10-05) · Oct 2026
· source
· release history
Provides MCP Authorization Tracing to diagnose authorization flow issues during Muse-to-gateway setup.
Aembit Launches Identity and Access Security Controls for Meta Muse (2026-10-05) · Oct 2026
· source
· release history
docs
Access Authorization Events now include the access.registration event type. It records each Dynamic Client Registration (DCR) request that an MCP client sends to the MCP Authorization Server.
docs update · Oct 2026
· source
Aembitâs access logs record more than âan MCP request happened.â They record that â âs Claude Desktop agent accessed Jira at 2:34 PM, received access under policy âJira-Readâ, and made 3 API calls.â
seen Oct 2026
· source
example
Attach CrowdStrike AIDR content inspection to a specific MCP Access Policy so that tool listings, inputs, and outputs are evaluated before the agent's request is allowed through.$ In the Aembit UI, open the target Access Policy, navigate to the 'Content Security' section, select CrowdStrike AIDR as the provider, and enable the checkpoints (tool listings, tool inputs, tool…
CrowdStrike AIDR Tells You What’s Risky. Aembit Tells You Who Gets Access. (2026-09-15) · Sep 2026
· source
+AI Agent Identity Management via MCP Authorization ServershippedProvides dedicated identity and policy enforcement for Model Context Protocol (MCP) workloads, supporting OAuth flows, session management, resource discovery, and real-time authorization tracing.22 releases · 1 other source · first seen Jan 2026▸
Also counts toward: MCP server
release
22 total
Read the MCP Identity Gateway version without an access token via the aembit_gateway_version field now present in the protected resource metadata document.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
changelog · Oct 2026
· source
· release history
MCP Identity Gateway now sends tool-argument request headers to MCP clients on earlier specification revisions when connecting to MCP servers on the 2026-07-28 MCP specification.
changelog · Oct 2026
· source
· release history
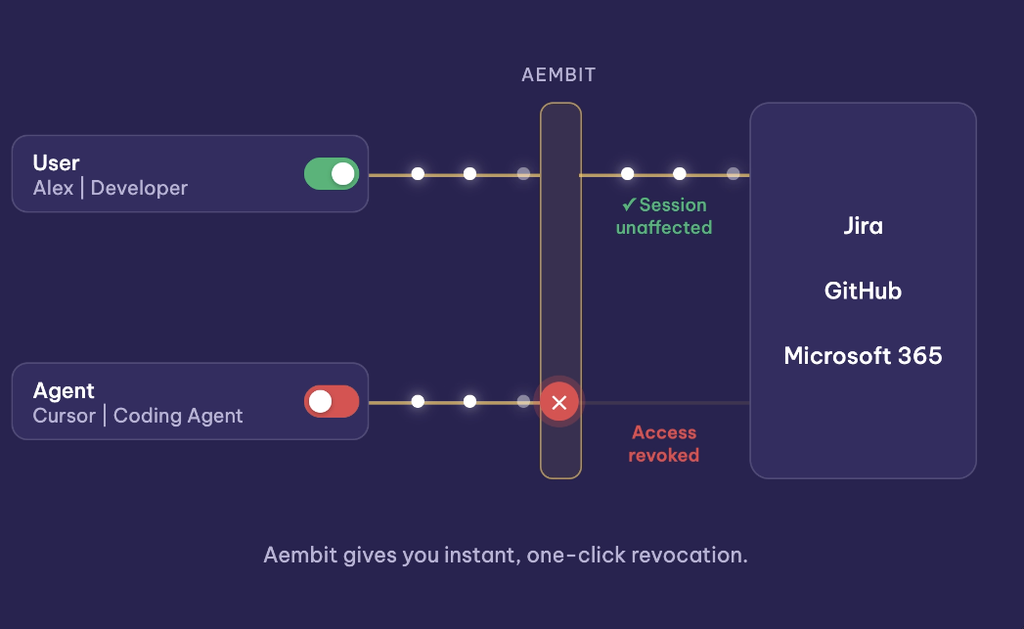
Revoke a specific MCP user session by navigating to Administration > Identity Providers > Sessions tab and selecting Revoke session, scoped to one user and one MCP client without affecting other sessions.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Introducing the AI Agent Kill Switch: Instant Single-User Revocation (2026-10-29) · Oct 2026
· source
· release history
Sessions appear for MCP clients that connect through a Client-to-Gateway Access Policy using an OIDC ID Token Credential Provider with refresh token support enabled; admins need Read/Write permission on Identity Providers to revoke.
Introducing the AI Agent Kill Switch: Instant Single-User Revocation (2026-10-29) · Oct 2026
· source
· release history
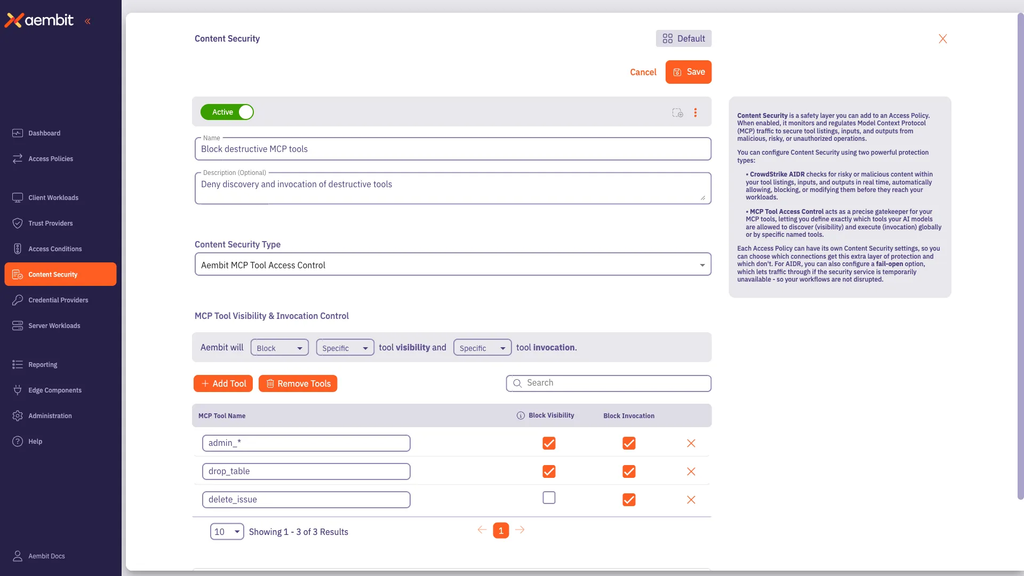
Introduces MCP Tool Access Control in the Aembit MCP Identity Gateway, enabling per-tool allow/block rules inside an access policy — controlling both tools/list discovery visibility and tools/call invocation independently.
Introducing MCP Tool Filtering: Fine-Grained, Least-Privilege Authorization for AI Agents (2026-10-15) · Oct 2026
· source
· release history
Adds MCP Identity Gateway as the termination point for Meta Muse agent connections, enabling runtime policy evaluation against access policies.
Aembit Launches Identity and Access Security Controls for Meta Muse (2026-10-05) · Oct 2026
· source
· release history
docs
An employee uses Claude Desktop to query Jira and search Confluence through an MCP server. Aembit authenticates the user through your IdP, identifies the agent by its workload identity, and issues a short-lived token scoped to both.
docs update · Oct 2026
· source
+Aembit CLIshippedA command-line interface for interacting with the Aembit platform, with installers for Linux and Windows that support runtime configuration of connection and keep-alive settings.15 releases · 5 other sources · first seen Jul 2025▸
Also counts toward: Command-line interface
release
15 total
Adds aws-access-key-id input to the Aembit GitHub Action (minimum version 1.3.0) so a workflow on a GitHub-hosted runner can select among multiple AWS STS Federation Credential Providers in a single Access Policy by Access Key ID selector.
changelog · Sep 2026
· source
· release history
Provides a common enforcement point for AI agent access to MCP servers, tools, and enterprise resources across both XAA and OAuth environments.
announced · seen Sep 2026
· source
· release history
Automatically falls back to the standard OAuth Authorization Code flow for any upstream MCP server or identity provider that doesn't support XAA, requiring no separate configuration.
How Aembit Makes Cross App Access Usable Before the Rest of the Stack Catches Up (2026-09-22) · Sep 2026
· source
· release history
Makes the integration configurable through the Aembit UI, API, or Terraform with no changes required to existing AIDR console configuration.
CrowdStrike AIDR Tells You What’s Risky. Aembit Tells You Who Gets Access. (2026-09-15) · Sep 2026
· source
· release history
Covers three MCP inspection checkpoints per policy — tool listings, tool inputs, and tool outputs — with AIDR returning an allow, block, or transform verdict that Aembit enforces inline.
CrowdStrike AIDR Tells You What’s Risky. Aembit Tells You Who Gets Access. (2026-09-15) · Sep 2026
· source
· release history
Adds aembit_agent_cli_linux_amd64_glibc_<version>.tar.gz as a second Linux amd64 archive in Aembit CLI 1.34.5772, dynamically linking against glibc 2.28 or newer, for organizations whose policy requires glibc or to work around DNS resolution issues caused by musl's stricter handling of resolver responses.
changelog · Aug 2026
· source
· release history
docs
Agent Proxy 1.34.6014 fixes the published Rust advisory RUSTSEC-2026-0258 in the bundled h2 HTTP/2 library. Aembit CLI has included the same fix since version 1.34.5772.
seen Oct 2026
· source
without changing how the Access Policyâs other components authorize access. - The set of MCP tools an MCP server advertises when an AI agent asks what MCP tools - The calls an AI agent makes to those MCP tools.
docs update · Sep 2026
· source
MCP Identity Gateway MCP Authorization Server Blended Identity Set up the MCP Identity Gateway Set up the MCP Authorization Server Aembit MCP Server Section titled âAembit MCP Serverâ This section covers the Aembit MCP Server, which exposes your Tenantâs configuration to an MCP client so you can query and manage…
docs update · Sep 2026
· source
: Content Security Providers govern the MCP tool traffic flowing through Aembit's MCP Identity Gateway. You add a provider to the Content Security component of an Access Policy. (how to govern MCP tool traffic) For MCP traffic, an Access Policy can also include a Content Security Provider.
docs update · Sep 2026
· source
example
Apply gRPC keep-alive settings at install time on Windows so the CLI maintains its tenant connection over idle periods.$ msiexec /i AembitCLI.msi AEMBIT_TENANT_GRPC_PING_INTERVAL_SECS=30 AEMBIT_TENANT_GRPC_PING_TIMEOUT_SECS=10
changelog · Aug 2026
· source
+Edge SDKshippedIn-process TypeScript and Python libraries that handle workload attestation, token lifecycle, and credential retrieval without requiring a proxy, suited for serverless functions, ephemeral CI containers, and restricted runtimes.17 releases · 2 other sources · first seen Jan 2024▸
Also counts toward: Agentless deployment, CI/CD pipeline integration, Python scripting support, Scripting language support, Client SDKs
release
17 total
Adds AWS Metadata Service, Azure Instance Metadata Service, GCP Identity Token, Kubernetes Service Account, and OIDC ID Token Trust Provider support to the Python Edge SDK (pip install aembit-edge-sdk, requires Python 3.10+).
changelog · Oct 2026
· source
· release history
Adds GitLab, Kubernetes Service Account, and Terraform Cloud Trust Provider support to the TypeScript Edge SDK, bringing both SDKs to parity across the same nine Trust Providers.
changelog · Oct 2026
· source
· release history
Adds new integration guides for Azure Functions, Azure virtual machines, GitHub Actions, GitLab CI/CD, Kubernetes, and Terraform Cloud, each covering both TypeScript and Python, and adds an Edge SDK logging reference documenting events the SDKs log, how to route them to a logger, and which hosts the SDKs contact.
changelog · Oct 2026
· source
· release history
Extends the Edge API credentials endpoint and Edge SDKs for TypeScript and Python (minimum Edge SDK 1.34.0) to pass an AWS STS Credential Provider selector as connection metadata alongside existing JWT Credential Provider selectors.
changelog · Sep 2026
· source
· release history
Extends policy-based access enforcement and auditability to Okta XAA-driven agent connections, letting security teams centrally control which agents act on whose behalf and under what policy.
announced · seen Sep 2026
· source
· release history
Aembit's Edge Controller brokers XAA between identity providers and upstream MCP servers that don't yet support XAA natively — generating and signing assertions using the tenant's own keys when the IdP cannot perform the exchange directly.
How Aembit Makes Cross App Access Usable Before the Rest of the Stack Catches Up (2026-09-22) · Sep 2026
· source
· release history
docs
Aembit Edge SDKs Aembit now offers Edge SDKs for TypeScript and Python, so your application can attest its workload and retrieve credentials in a few method calls. Explore the Edge SDKs Developer Guide Integrate from code, commands, or infrastructure.
seen Aug 2026
· source
example
Install the new Aembit Python Edge SDK on a Python 3.10+ workload to unlock all nine Trust Providers.$ pip install aembit-edge-sdk
changelog · Oct 2026
· source
+Identity and Access Management IntegrationshippedSupports diverse identity providers including OIDC, SAML, Kerberos, and service accounts for GitLab, AWS, and Kubernetes workloads.17 releases · 2 other sources · first seen Jul 2025▸
release
17 total
Adds ${saml.response.issuer} expression to dynamic claims to return the identity provider issuer from a SAML assertion.
Dynamic claims now support SAML assertions · Sep 2026
· source
· release history
Adds the ability to configure multiple OIDC Endpoint values in a single Trust Provider via the Add an Endpoint action, allowing validation of service account tokens signed by different cluster issuers.
Kubernetes Service Account Trust Provider now supports multiple OIDC endpoints · Sep 2026
· source
· release history
Enhanced: User name resolution logic in automatic SSO user creation now explicitly supports standard OpenID Connect (OIDC) profile claims.
Automatic user creation reads user names from more claims · Sep 2026
· source
· release history
Adds ${saml.response.attributes['<name>']} expression to dynamic claims to return specific attributes (e.g., groups) from a SAML assertion.
Dynamic claims now support SAML assertions · Sep 2026
· source
· release history
Adds ${saml.response.subject.nameId} expression to dynamic claims to return the Subject NameID from a SAML response.
Dynamic claims now support SAML assertions · Sep 2026
· source
· release history
Introduces the GCP IAP JWT Trust Provider type to validate signed x-goog-iap-jwt-assertion tokens from Google Cloud IAP on GKE, Cloud Run, or App Engine.
Google Cloud Identity-Aware Proxy (IAP) JWT Trust Provider now available · Aug 2026
· source
· release history
example
Bind an issued credential to the user's unique identity found in the SAML NameID field.$ ${saml.response.subject.nameId}
Dynamic claims now support SAML assertions · Sep 2026
· source
Read the identity provider that issued the SAML assertion.$ ${saml.response.issuer}
Dynamic claims now support SAML assertions · Sep 2026
· source
+Workload Identity Federation for AI APIsshippedAllows workloads to authenticate to Anthropic Claude and OpenAI ChatGPT APIs using short-lived federation tokens derived from OIDC-compliant identity sources, eliminating static API keys.11 releases · 4 other sources · first seen Jun 2026▸
Shared capability: OIDC SSO
Also counts toward: Terraform provider
release
11 total
Extends Aembit's WIF credential provider ecosystem to now cover AWS STS, Azure Entra, GCP, Anthropic Claude, and OpenAI ChatGPT under a single secretless access policy model.
OpenAI Workload Identity Federation: Aembit Brings Secretless Access to the OpenAI API (2026-08-17) · Aug 2026
· source
· release history
Adds the OpenAI WIF credential provider in Aembit Cloud v1.33, enabling workloads to authenticate to the OpenAI ChatGPT API with short-lived, scoped access tokens instead of static sk-proj-... API keys.
OpenAI Workload Identity Federation: Aembit Brings Secretless Access to the OpenAI API (2026-08-17) · Aug 2026
· source
· release history
The EdgeController intercepts outbound OpenAI API requests at runtime, exchanges an Aembit-issued federation token at OpenAI's token endpoint, and injects the resulting short-lived access token — requiring no application code changes, SDK modifications, or credential management logic.
OpenAI Workload Identity Federation: Aembit Brings Secretless Access to the OpenAI API (2026-08-17) · Aug 2026
· source
· release history
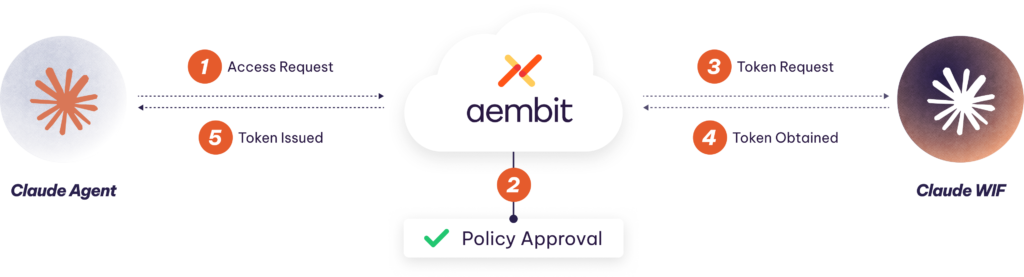
Extends Aembit's existing Workload Identity Federation Credential Provider pattern (previously covering AWS STS, Azure Entra, and GCP) to include Anthropic's Claude API, allowing any OIDC-compliant identity source (AWS IAM, Google Cloud, Microsoft Entra ID, GitHub Actions, Kubernetes service accounts, SPIFFE, Okta) to…
Aembit Adds Workload Identity Federation Support for the Claude API (2026-08-05) · Aug 2026
· source
· release history
Aembit's EdgeController now transparently performs the federation token exchange against Claude's POST /v1/oauth/token OAuth endpoint and injects the resulting short-lived bearer token into outbound requests — no application code changes required.
Aembit Adds Workload Identity Federation Support for the Claude API (2026-08-05) · Aug 2026
· source
· release history
Adds a claude_wif block to the Aembit Terraform Provider, with required arguments federation_rule_id, organization_id, and service_account_id, and optional arguments audience, scope, workspace_id, and lifetime.
Aembit Adds Workload Identity Federation Support for the Claude API (2026-08-05) · Aug 2026
· source
· release history
docs
Enhanced security for the OAuth 2.0 Authorization Code Credential Dynamic claims can now read values from a SAML 2.0 response, so a Credential Provider can issue a credential bound to each SAML userâs own identity.
docs update · Sep 2026
· source
example
Bind a SAML user's group membership into a dynamically issued credential so each user gets a credential scoped to their own identity.$ ${saml.response.attributes['groups']}
changelog · Sep 2026
· source
Verify that a newly configured Claude WIF Credential Provider can successfully exchange tokens with Claude's OAuth endpoint before attaching it to a policy.$ # In the Aembit Admin Portal: # 1. Go to Credential Providers # 2. Select the Claude WIF Credential Provider you created # 3.
Aembit Adds Workload Identity Federation Support for the Claude API (2026-08-05) · Aug 2026
· source
Provision a Claude WIF Credential Provider in Terraform so workloads get short-lived Claude tokens instead of static sk-ant-… keys.$ resource "aembit_credential_provider" "claude_wif" { name = "claude-wif-prod" claude_wif = { federation_rule_id = "fdrl_xxxxxxxxxxxxxxxx" organization_id = "xxxxxxxx-xxxx-xxxx-xxxx-xxxxxxxxxxxx"…
Aembit Adds Workload Identity Federation Support for the Claude API (2026-08-05) · Aug 2026
· source
+Content security for MCP tool trafficshippedGoverns Model Context Protocol tool traffic flowing through the MCP Identity Gateway via Content Security Providers that inspect tool listings, inputs, and outputs.11 releases · 3 other sources · first seen Aug 2026▸
release
11 total
MCP Identity Gateway now accepts an access token for up to 3 seconds after expiry, down from 60 seconds — MCP clients must refresh access tokens before they expire.
changelog · Oct 2026
· source
· release history
Adds subscriptions_workload_refresh_interval timeout setting (default: 30 seconds) to MCP Identity Gateway, controlling how often it checks for assignment and rule changes, and extends it to relay subscriptions/listen change notifications to MCP clients using the 2026-07-28 MCP specification revision, including…
changelog · Oct 2026
· source
· release history
The status field in MCP client error data (sent when MCP Identity Gateway cannot connect to an MCP server) is replaced by upstreamHttpStatus — update any client code that reads status.
changelog · Oct 2026
· source
· release history
Adds application.mcp.contentSecurity.toolFilter audit event that records which rule matched and why for every filtered tools/list response or blocked tools/call request.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Introducing MCP Tool Filtering: Fine-Grained, Least-Privilege Authorization for AI Agents (2026-10-15) · Oct 2026
· source
· release history
Adds the ability to attach CrowdStrike AIDR content security configurations to specific MCP access policies within Aembit
CrowdStrike AIDR Tells You What’s Risky. Aembit Tells You Who Gets Access. (2026-09-15) · Sep 2026
· source
· release history
Correlates every CrowdStrike AIDR finding with Aembit's identity and policy context (agent, target MCP server, applicable policy, Content Security decision) in a single workload event.
CrowdStrike AIDR Tells You What’s Risky. Aembit Tells You Who Gets Access. (2026-09-15) · Sep 2026
· source
· release history
docs
The Gateway-to-Server policy authorizes the Identity Gateway to reach a specific MCP server and uses a Because the userâs identity rides in every request, the Identity Gateway extends across both hops, combining the human user and the AI agent in a single access decision.
seen Oct 2026
· source
MCP Identity Gateway version 1.34.6034 validates more access tokens and reports conflicting tool and prompt names. It also changes which timeout names take effect and what its request duration metric measures. ES256-signed access tokens : MCP Identity Gateway validates access tokens signed with ES256 as well as RS256.
docs update · Oct 2026
· source
example
Attach CrowdStrike AIDR content inspection to a specific MCP Access Policy so that tool listings, inputs, and outputs are evaluated before the agent's request is allowed through.$ In the Aembit UI, open the target Access Policy, navigate to the 'Content Security' section, select CrowdStrike AIDR as the provider, and enable the checkpoints (tool listings, tool inputs, tool…
CrowdStrike AIDR Tells You What’s Risky. Aembit Tells You Who Gets Access. (2026-09-15) · Sep 2026
· source
+CrowdStrike AIDR MCP content inspectionshippedIntegrates CrowdStrike Falcon AI Detection and Response (AIDR) into Aembit access policies to inspect MCP tool listings, inputs, and outputs for AI agent traffic, with configurable allow, block, report, or transform actions and fail-open/fail-closed behavior per policy.11 releases · 2 other sources · first seen Sep 2026▸
Also counts toward: ML-based detection
release
11 total
Enforces CrowdStrike AIDR allow, block, or transform verdicts in the same request path as identity and access policy evaluation for tool listings, inputs, and outputs
CrowdStrike AIDR Tells You What’s Risky. Aembit Tells You Who Gets Access. (2026-09-15) · Sep 2026
· source
· release history
New integration with CrowdStrike Falcon AI Detection and Response (AIDR) enables inspection of MCP tool listings, inputs, and outputs for AI agent traffic governed by Aembit.
announced · seen Sep 2026
· source
· release history
Configurable policies on MCP interactions support allow, report, block, or transform actions based on identity context and risks identified by CrowdStrike AIDR.
announced · seen Sep 2026
· source
· release history
Aembit MCP Identity Gateway allows centrally pre-configured CrowdStrike AIDR policies to be applied across all MCP clients without per-client configuration or custom agent-side inspection logic.
announced · seen Sep 2026
· source
· release history
Aembit supplies run-time identities for user-delegated and autonomous agents to CrowdStrike AIDR, enriching AIDR policy decisions with workload identity context.
announced · seen Sep 2026
· source
· release history
CrowdStrike AIDR findings now link directly to corresponding Aembit access records, enabling investigators to pivot between platforms without manually reconciling separate logs.
announced · seen Sep 2026
· source
· release history
example
Use the UI to attach CrowdStrike AIDR configuration to a specific MCP connection's access policy.$ In the Aembit console, go to Access Policies > [Policy Name] > Content Security and select 'CrowdStrike AIDR'.
CrowdStrike AIDR Tells You What’s Risky. Aembit Tells You Who Gets Access. (2026-09-15) · Sep 2026
· source
Attach a CrowdStrike AIDR content security configuration to a sensitive MCP access policy via the Aembit UI so that tool listings, inputs, and outputs are inspected before reaching your AI agent.$ In the Aembit console, open the target Access Policy > Content Security > attach a CrowdStrike AIDR content security configuration > set fail behavior to 'fail-closed' > Save.
Aembit + CrowdStrike: More Judgment Behind Every AI Agent “Yes” (2026-09-01) · Sep 2026
· source
+Kubernetes workload identity and certificate managementshippedManages workload identity through Kubernetes Service Account attestation across clusters and issues mTLS certificates via the Secrets Operator without private keys leaving the cluster.10 releases · 1 other source · first seen Feb 2025▸
Also counts toward: Kubernetes-native deployment
release
10 total
Allows a Kubernetes Service Account Trust Provider to accept multiple OIDC endpoints (one per cluster issuer URL, added via Add an Endpoint), enabling attestation of a single Client Workload running active-active across two or more clusters.
changelog · Sep 2026
· source
· release history
Secrets Operator now writes certificates to kubernetes.io/tls Secret types (with tls.crt and tls.key fields) when using the X509Svid credential type
Aembit Secrets Operator now delivers X.509-SVID certificates · Sep 2026
· source
· release history
Aembit Secrets Operator 1.31.314 updates its CRDs to v1 API.
Aembit Secrets Operator CRDs graduate to v1 · May 2026
· source
· release history
Adds custom annotation support on Kubernetes resources in the Helm chart
Edge components release with OpenShift support and AWS Secrets Manager private n · Aug 2025
· source
· release history
Adds Official Red Hat OpenShift and ROSA support for Agent Proxy and Sidecar Init, including SecurityContextConstraint configurations
Edge components release with OpenShift support and AWS Secrets Manager private n · Aug 2025
· source
· release history
Enables wildcard hostname support for Server Workloads in Agent Controller.
Aembit CLI, AWS Secrets Manager, and Jenkins Pipelines now available · Jul 2025
· source
· release history
example
Issue mTLS certificates to a workload without the private key ever leaving the cluster — Secrets Operator handles CSR generation and automatic renewal.$ credentialType: X509Svid
changelog · Sep 2026
· source
+Tool Filtering and Access Scoping for MCP TrafficshippedEnables configurable allow or block mode enforcement for MCP tool access using exact names and glob patterns, scoping permissions by blended identity and evaluating filtering rules before deeper inspection to enforce fail-closed defaults.6 releases · 1 other source · first seen Oct 2026▸
release
MCP clients now receive MCP server errors directly when MCP Tool Access Control is filtering a tool list and the upstream MCP server returns an error.
changelog · Oct 2026
· source
· release history
Enforces tool-filtering rules in Allow mode (deny unmatched by default) or Block mode (permit unmatched by default), selectable per policy to match least-privilege or low-maintenance postures.
Introducing MCP Tool Filtering: Fine-Grained, Least-Privilege Authorization for AI Agents (2026-10-15) · Oct 2026
· source
· release history
Scopes tool-access rules by blended identity — user identity, group membership, and workload/agent identity — so different principals sharing the same MCP server receive different tool sets.
Introducing MCP Tool Filtering: Fine-Grained, Least-Privilege Authorization for AI Agents (2026-10-15) · Oct 2026
· source
· release history
Supports exact tool names and glob patterns (e.g., get_user*, admin_*, list_*, delete_*) in tool-filtering policies so new tools inherit rules automatically without manual allow-list updates.
Introducing MCP Tool Filtering: Fine-Grained, Least-Privilege Authorization for AI Agents (2026-10-15) · Oct 2026
· source
· release history
Fails closed by default: a missing or malformed tool-filtering policy causes the gateway to return an empty tools/list and block tools/call, never failing open.
Introducing MCP Tool Filtering: Fine-Grained, Least-Privilege Authorization for AI Agents (2026-10-15) · Oct 2026
· source
· release history
Evaluates tool-filtering policy before deeper inspection layers (e.g., CrowdStrike AIDR), resolving coarse-grained discovery and invocation decisions first in the enforcement chain.
Introducing MCP Tool Filtering: Fine-Grained, Least-Privilege Authorization for AI Agents (2026-10-15) · Oct 2026
· source
· release history
example
Lock a read-only customer-support agent to only list_ tools on a GitHub MCP server, blocking all write and delete tools by glob pattern.$ In the Aembit console, open your access policy for the customer-support agent, enable MCP Tool Access Control, set mode to 'Allow', and add the rule: Tool pattern: list_* Leave all other tools…
Introducing MCP Tool Filtering: Fine-Grained, Least-Privilege Authorization for AI Agents (2026-10-15) · Oct 2026
· source
+XAA broker and support for unsupported identity providersshippedGenerates and signs Cross App Access (XAA) assertions to bridge enterprise identity providers with upstream MCP servers that do not natively support the protocol.6 releases · 1 other source · first seen Sep 2026▸
release
Adds Sessions tab to each Identity Provider in the Aembit Tenant UI, listing active MCP user sessions with the ability to filter, revoke individual sessions, or revoke all sessions for a user or MCP client at once.
changelog · Oct 2026
· source
· release history
Supports Meta Muse Dynamic Client Registration against the Aembit authorization server — no manual app creation, client ID, or secret required.
Aembit Launches Identity and Access Security Controls for Meta Muse (2026-10-05) · Oct 2026
· source
· release history
Enables Muse to connect to the MCP Identity Gateway by requesting the gateway URL as an OAuth scope, matching the gateway's protected-resource metadata advertisement.
Aembit Launches Identity and Access Security Controls for Meta Muse (2026-10-05) · Oct 2026
· source
· release history
Automatically falls back to the standard OAuth Authorization Code flow for any upstream MCP server or identity provider that doesn't support XAA, requiring no separate configuration.
How Aembit Makes Cross App Access Usable Before the Rest of the Stack Catches Up (2026-09-22) · Sep 2026
· source
· release history
Enables Aembit to broker authorization between XAA and existing OAuth standards, allowing zero-touch agent access even when upstream MCP servers or IdPs lack native XAA support.
How Aembit Makes Cross App Access Usable Before the Rest of the Stack Catches Up (2026-09-22) · Sep 2026
· source
· release history
Aembit's Edge Controller brokers XAA between identity providers and upstream MCP servers that don't yet support XAA natively — generating and signing assertions using the tenant's own keys when the IdP cannot perform the exchange directly.
How Aembit Makes Cross App Access Usable Before the Rest of the Stack Catches Up (2026-09-22) · Sep 2026
· source
· release history
example
Revoke all active MCP sessions for a compromised user without deleting the Identity Provider.$ In the Aembit Tenant UI, go to Identity Providers > <your IdP> > Sessions, filter by the user, then select 'Revoke all sessions for this user'.
changelog · Oct 2026
· source
+Agent and Proxy Runtime ConfigurationshippedOffers environment variable controls for logging, process identification, port management, and registration timing for Agent Proxy and Controller components.7 releases · first seen May 2025▸
release
7 total
AEMBIT_TENANT_GRPC_PING_INTERVAL_SECS and AEMBIT_TENANT_GRPC_PING_TIMEOUT_SECS environment variables configure gRPC keep-alives for Agent Proxy reconnects. Keep-alives are off by default.
Edge components release with reliability and CLI enhancements · Jun 2026
· source
· release history
AEMBIT_HTTP_IDLE_TIMEOUT_SECS configures the HTTP idle timeout on Windows in the Agent Proxy.
Edge components release with reliability and CLI enhancements · Jun 2026
· source
· release history
Oracle Database protocol support is now generally available, including mid-connection TLS and Prometheus metrics for credential injection events.
Edge components release with Oracle GA and HTTP proxy support · May 2026
· source
· release history
Agent Proxy now honors HTTP_PROXY, HTTPS_PROXY, and NO_PROXY environment variables to route outbound connections through an HTTP proxy.
Agent Proxy now honors HTTP proxy environment variables · Apr 2026
· source
· release history
Adds HTTP_PROXY, HTTPS_PROXY, and NO_PROXY environment variable support to Agent Controller for configuring outbound proxy routes
Agent Controller now honors HTTP proxy environment variables · Apr 2026
· source
· release history
Adds AEMBIT_HTTP_PORT_DISABLED environment variable to disable Agent Controller's HTTP port
Kerberos and PKI security enhancements for Agent Proxy · Jun 2025
· source
· release history
+Meta Muse MCP gateway integrationshippedConnects Meta Muse to the MCP Identity Gateway via OAuth Dynamic Client Registration and a generated skill file, enabling authenticated tool discovery and invocation without manual client credential setup.3 releases · 2 other sources · first seen Oct 2026▸
Also counts toward: Python scripting support
release
Supports the Aembit MCP Identity Gateway for enforcing identity and policy on personal AI agents such as Meta Muse, with integration into other gateways already in use.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Personal AI Agents Are Here, and Aembit Customers Can Secure Them Today (2026-10-05) · Oct 2026
· source
· release history
Enables Dynamic Client Registration for Meta Muse OAuth clients, allowing the agent to register without manual client ID/secret creation.
Aembit Launches Identity and Access Security Controls for Meta Muse (2026-10-05) · Oct 2026
· source
· release history
Generates a reusable Muse skill file (e.g. ~/workspace/skills/aembit-mcp-gateway/bin/mcp.py) using CREDENTIAL_NAME, MCP_URL, and ALLOWED_HOSTS constants, enabling persistent tools/list and tools/call invocations through the gateway.
Aembit Launches Identity and Access Security Controls for Meta Muse (2026-10-05) · Oct 2026
· source
· release history
example
Verify the Muse-to-gateway connection and confirm tool availability by calling tools/list after the OAuth flow completes.$ In the Muse chat window, type: 'connect my Aembit MCP gateway'. After Dynamic Client Registration and the OAuth flow complete, Muse will invoke tools/list against…
Aembit Launches Identity and Access Security Controls for Meta Muse (2026-10-05) · Oct 2026
· source
Configure a Meta Muse skill file to route tool calls through the Aembit MCP Identity Gateway using tenant-specific URLs.$ # ~/workspace/skills/aembit-mcp-gateway/bin/mcp.py CREDENTIAL_NAME = "custom.aembit-mcp-gateway" MCP_URL = "https://<tenant>.mcpgateway.aembit.io/mcp" ALLOWED_HOSTS =…
Aembit Launches Identity and Access Security Controls for Meta Muse (2026-10-05) · Oct 2026
· source
+Certificate Authority and Trust ManagementshippedManages dedicated Certificate Authorities, certificate chain delivery, and custom trust boundaries for isolated security domains.5 releases · first seen Mar 2025▸
release
On Windows, Agent Controller now installs intermediate CA certificates from its TLS certificate chain into the LocalMachine certificate store
Agent Controller 1.34.3725 release · Sep 2026
· source
· release history
Changes Trust Provider attestation failure severity from Warning to Error
Expanded MCP and AI IAM event coverage · May 2026
· source
· release history
Adds AEMBIT_LOG_LEVEL environment variable to control Agent Injector logging verbosity
Improved Agent Injector pod security and TLS handling · May 2025
· source
· release history
Enhances TLS certificate handling within the Agent Injector
Improved Agent Injector pod security and TLS handling · May 2025
· source
· release history
Adds Standalone CAs feature to create dedicated Certificate Authorities independent of Tenant-level certificates for isolated trust boundaries.
Standalone CAs and Credential Provider Integrations now available · Mar 2025
· source
· release history
+Gateway Health and Metrics ExposureshippedProvides operational visibility through HTTP health endpoints returning status codes and Prometheus metrics for gateway and credential injection events.5 releases · first seen May 2026▸
release
Exposes nine new Prometheus metrics tracking upstream fanout behavior, authentication failures, JWKS refreshes, session cleanup, and readiness probe stability.
MCP Identity Gateway 1.34.5733 release · Aug 2026
· source
· release history
Updates the Gateway's metrics reference to document all 20 MCP-specific metrics with types, labels, and label values.
MCP Identity Gateway 1.34.5733 release · Aug 2026
· source
· release history
Exposes application-scoped Prometheus metrics for MCP Identity Gateway observability.
MCP Identity Gateway 1.31.4955 release · May 2026
· source
· release history
Adds Prometheus metrics for MCP protocol-level errors and request failures.
MCP Identity Gateway 1.31.4955 release · May 2026
· source
· release history
Provides Prometheus metrics (aembit_agent_proxy_credential_injections_total with application_protocol="oracleDatabase") for monitoring Oracle credential injection events.
Oracle Database now generally available · May 2026
· source
· release history
+Workload Discovery and VisibilityshippedAutomatically identifies and discovers workloads across infrastructure using native agents or external integrations like Wiz.5 releases · first seen Apr 2025▸
release
Expands Wiz Discovery integration to discover Client Workload resources including VMs, AWS Client Workload Identifies, and Azure Client Workload Identifies.
Aembit Edge API now available with expanded Wiz Discovery · Jun 2025
· source
· release history
Expands Wiz Discovery integration to discover Server Workload resources including Azure Blob Storage and GCP BigQuery.
Aembit Edge API now available with expanded Wiz Discovery · Jun 2025
· source
· release history
Adds Discovery feature to automatically identify workloads across infrastructure for improved visibility, scalability, and access control
Workload Discovery now available · Apr 2025
· source
· release history
Adds Wiz integration as a supported source for workload discovery
Workload Discovery now available · Apr 2025
· source
· release history
Adds Aembit Edge Discovery as a native source for finding workloads
Workload Discovery now available · Apr 2025
· source
· release history
+MCP Session RevocationshippedAllows operators to revoke individual or bulk MCP sessions by user email or MCP client — including via API for incident-response automation — without affecting unrelated users or agents.2 releases · 2 other sources · first seen Oct 2026▸
Also counts toward: REST API, Scripting API, Web management console
release
Filter and bulk-revoke sessions in the Sessions view by user email, MCP client, or both using Revoke filtered, covering all sessions for one user or all sessions for one MCP client.
Introducing the AI Agent Kill Switch: Instant Single-User Revocation (2026-10-29) · Oct 2026
· source
· release history
Automate session revocation in incident-response workflows via the Aembit Cloud API.
Introducing the AI Agent Kill Switch: Instant Single-User Revocation (2026-10-29) · Oct 2026
· source
· release history
example
Immediately cut off a single user's compromised Claude Code session without locking them out of other agents or breaking the tool for teammates.$ In your Aembit tenant: 1. Go to Administration > Identity Providers and open the provider your users sign in through. 2. Open the Sessions tab. 3.
Introducing the AI Agent Kill Switch: Instant Single-User Revocation (2026-10-29) · Oct 2026
· source
Bulk-revoke all sessions tied to a retired MCP client during incident response, without touching any other user or agent.$ In your Aembit tenant: 1. Go to Administration > Identity Providers, open the relevant provider, and open the Sessions tab. 2. Filter by the retired MCP client name. 3.
Introducing the AI Agent Kill Switch: Instant Single-User Revocation (2026-10-29) · Oct 2026
· source
+Proactive Credential RenewalshippedAutomatically refreshes credentials at 80% of their TTL or a configurable interval to ensure availability.4 releases · first seen May 2026▸
release
Issues SPIFFE-compliant X.509-SVID certificates for end-to-end mTLS between workloads via Agent Proxy, CLI, or Aembit Secrets Operator (Kubernetes), with certificates auto-rotating at 80% of their lifetime (15-minute default, configurable) and private keys never persisted to disk.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Aembit Now Supports SPIFFE: X.509-SVID and JWT-SVID Without SPIRE (2026-10-27) · Oct 2026
· source
· release history
Implements background token refresh logic that proactively updates ID and refresh tokens captured at SSO login, preventing slow round-trip exchanges during request time.
How Aembit Makes Cross App Access Usable Before the Rest of the Stack Catches Up (2026-09-22) · Sep 2026
· source
· release history
Enables automatic certificate renewal for X.509-SVID identities by refreshing secrets before expiration
Aembit Secrets Operator now delivers X.509-SVID certificates · Sep 2026
· source
· release history
Enables proactive credential renewal where credentials refresh at 80% of their TTL, or sooner when you configure a shorter refreshInterval
Aembit Secrets Operator now available · May 2026
· source
· release history
+Server Workload mTLS AuthenticationshippedAllows Server Workloads to validate client identities using SPIFFE-compliant X.509-SVID certificates via mTLS.4 releases · first seen May 2026▸
release
Adds X509Svid as a new value for credentialType in AembitSecretRefreshSchedule to generate private keys and signed certificates inside the cluster
Aembit Secrets Operator now delivers X.509-SVID certificates · Sep 2026
· source
· release history
X.509-SVID retrieval generates the CSR locally and returns the signed certificate chain in CLIENT_CERT_CHAIN.
Aembit CLI now retrieves X.509-SVID certificates · Jun 2026
· source
· release history
Enables Agent Proxy to establish outbound mTLS connections to Server Workloads using SPIFFE-compliant X.509-SVID certificates generated in memory.
End-to-end mTLS between Client and Server Workloads with SPIFFE X.509-SVID certi · May 2026
· source
· release history
Adds mTLS Authentication method with the x509 Certificate scheme to Server Workloads for validating client certificates.
End-to-end mTLS between Client and Server Workloads with SPIFFE X.509-SVID certi · May 2026
· source
· release history
+Secure Transport and Proxy FeaturesshippedEnhances secure communication through transparent AWS S3 upload signing, TLS handling improvements, and Kubernetes compatibility updates.4 releases · first seen May 2025▸
release
AGENT_TRUST_PATH again supports supplying a custom CA certificate for Agent Proxy connections to Aembit Cloud.
Edge components release with reliability and CLI enhancements · Jun 2026
· source
· release history
Enables independent TLS configuration on client-to-proxy and proxy-to-database connections for Oracle Server Workloads.
Oracle Database now generally available · May 2026
· source
· release history
Agent Proxy now supports transparent AWS S3 file uploads with automatic detection of signing methods via the x-amz-content-sha256 header.
Edge components release with AWS S3 uploads and multiple AWS STS support · Dec 2025
· source
· release history
Improves compatibility with securityContext settings in Kubernetes pod specs
Improved Agent Injector pod security and TLS handling · May 2025
· source
· release history
+Agent Controller Proxy RoutingshippedConfigures outbound proxy routing for Agent Controller and Agent Proxy components via standard environment variables.3 releases · first seen Apr 2026▸
release
Agent Controller now bypasses an HTTP proxy when calling the AWS instance metadata service for AWS Metadata Service Trust Provider attestation, matching its existing Azure behavior.
changelog · Oct 2026
· source
· release history
Agent Proxy now honors HTTP_PROXY, HTTPS_PROXY, and NO_PROXY environment variables to route outbound connections through an HTTP proxy.
Agent Proxy now honors HTTP proxy environment variables · Apr 2026
· source
· release history
Adds HTTP_PROXY, HTTPS_PROXY, and NO_PROXY environment variable support to Agent Controller for configuring outbound proxy routes
Agent Controller now honors HTTP proxy environment variables · Apr 2026
· source
· release history
+Personal AI agent identity and policy managementshippedAssigns each personal AI agent its own distinct agentic identity and extends existing Aembit access policies to cover personal AI agents across Microsoft 365, GitHub, and custom services, enabling independent credential issuance, scoping, and per-agent revocation without affecting the sponsoring employee.3 releases · first seen Oct 2026▸
release
Assigns each personal AI agent its own distinct agentic identity — separate from the sponsoring employee's login — so credentials can be issued, scoped, and revoked independently.
Personal AI Agents Are Here, and Aembit Customers Can Secure Them Today (2026-10-05) · Oct 2026
· source
· release history
Extends existing Aembit policy coverage to personal AI agents across Microsoft 365, GitHub, and custom in-house services under one unified policy model, at no extra cost.
Personal AI Agents Are Here, and Aembit Customers Can Secure Them Today (2026-10-05) · Oct 2026
· source
· release history
Provides a per-agent kill switch that revokes all access for a specific agent instantly across Microsoft 365, GitHub, and custom services without disrupting the employee.
Personal AI Agents Are Here, and Aembit Customers Can Secure Them Today (2026-10-05) · Oct 2026
· source
· release history
+Policy Compliance ReportingshippedProvides centralized visibility into security enforcement status with tiered compliance metrics and filtering for discovered workloads.3 releases · first seen May 2025▸
release
Introduces a new Global Policy Compliance page under Reporting in the left nav menu for viewing Access Policies compliance status.
Workload Discovery filtering and Global Policy Compliance reporting now availabl · Jun 2025
· source
· release history
Adds comprehensive filtering to Workload Discovery pages allowing search by Client Workload Identifiers, Workload Discovery Source, Port, and Protocol.
Workload Discovery filtering and Global Policy Compliance reporting now availabl · Jun 2025
· source
· release history
Introduces Global Policy Compliance for centralized security enforcement with Required, Recommended, and Optional tiers via color-coded status icons
Global Policy Compliance, OIDC ID Token Credential Provider, and Splunk Log Stre · May 2025
· source
· release history
+Oracle Database Credential InjectionshippedEnables secure, dynamic credential injection for Oracle Database 19c and 21c workloads, eliminating static passwords.2 releases · first seen May 2026▸
release
Oracle Database protocol support is now generally available, including mid-connection TLS and Prometheus metrics for credential injection events.
Edge components release with Oracle GA and HTTP proxy support · May 2026
· source
· release history
Adds production-ready Oracle Database protocol support (19c and 21c) to eliminate static database passwords via credential injection.
Oracle Database now generally available · May 2026
· source
· release history
+Agentless SPIFFE identity and policy evaluationshippedHandles SPIFFE identity attestation, credential issuance, and policy evaluation directly from the Aembit control plane, requiring no SPIRE server, agent, or supporting infrastructure.1 release · first seen Oct 2026▸
Also counts toward: Agentless deployment
release
Handles SPIFFE identity attestation, credential issuance, and policy evaluation directly from the Aembit control plane, requiring no SPIRE server, agent, or supporting infrastructure.
Aembit Now Supports SPIFFE: X.509-SVID and JWT-SVID Without SPIRE (2026-10-27) · Oct 2026
· source
· release history
+SPIFFE JWT-SVID issuanceshippedIssues SPIFFE JWT-SVID bearer tokens for workload authentication behind service meshes such as Istio and Envoy, handling standard JWT claims automatically and supporting custom claims built from literal values or dynamic workload attributes.1 release · first seen Oct 2026▸
release
Issues SPIFFE JWT-SVID tokens for bearer-token authentication behind service meshes such as Istio and Envoy, automatically handling standard claims (sub, iss, aud, exp, iat, jti) and supporting custom claims built from literal values or dynamic workload attributes (Kubernetes namespace, AWS account ID,…
Aembit Now Supports SPIFFE: X.509-SVID and JWT-SVID Without SPIRE (2026-10-27) · Oct 2026
· source
· release history
+AWS S3 Streaming Upload SupportshippedSupports large file uploads to AWS S3 via streaming chunked signing, removing previous size limits.1 release · first seen May 2026▸
release
Large file uploads to AWS S3 Log Streams are now supported via streaming AWS chunked signing, removing the previous upload size limit.
Edge components release with Oracle GA and HTTP proxy support · May 2026
· source
· release history
+Linux Workload Identity ExpansionshippedExpands workload identity matching for Linux VM deployments to include process command line and executable path identifiers.1 release · first seen Feb 2026▸
release
Adds Process Command Line and Process Path Client Workload identifiers for Linux VM deployments, with wildcard matching for command lines and exact executable-path matching.
Oracle Database support enters beta with new process-based identifiers · Feb 2026
· source
· release history
+Enhanced Private Network Access for Credential ProvidersshippedExtends Private Network Access capabilities to AWS Secrets Manager and HTTP Basic Auth providers, enabling secret retrieval from private VPCs.1 release · first seen Jan 2026▸
release
private network access support for HTTP Basic Auth Credential Providers using AWS Secrets Manager
Edge components release with S3 streaming and Secrets Manager improvements · Jan 2026
· source
· release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
5 commands for Aembit, each
with where it came from. This tool has no source analysis yet, so there
is no option reference and no captured run beside them.
View
Source
No command matches.
Screenshots
From the release notes, newest first. Click one to see it full size.
Breaking-change disciplinehow rarely a release breaks users, and notice given
Maintenance riskquiet time against its own cadence, maintainers
Innovation & surfacenew capabilities, API and MCP surface
Five scores for Aembit, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Each score is 0–100 on a published rubric, derived from data this site already shows.
A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
Documentation quality — the release-notes rubric published on the analytics page, unchanged.
Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Aembit puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
21 readings of Aembit's pricing page since Mar 2023, with 2 relaunches of its plan lineup and 5 changes to what its plans include — each one dated, compared with the reading before it, and explained for someone buying the tool.
Pricing and packaging history is included with Researcher and Business. See how every vendor we track sells, and how that has changed over time, using data we don't publish anywhere else.
Each offering on the pricing page links to its own page of plans, read at its latest capture.
Plan relaunches
Plans, prices and descriptions are quoted from the vendor's own pricing page as we read it on each date.
A plan missing from a later reading is shown as no longer listed on the page — a statement about the page, not the product.
Readings that failed to show any plans are left out rather than read as a change.
Website history
aembit.io, every change
Aembit's home and pricing pages and 30 more pages as they looked each month from September 2022 to October 2026: 77 renders, 16 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
What Aembit connects to, runs on and detects, read from its release notes and docs. So far: 2 new integrations, 2 updated integrations, 2 new supported platforms.
Show
When
6 changes, tracked since Oct 5, 2026.
Oct 142026
newSnyk integration for workload security posture
a recent security scan (for example, through the Snyk integration) shows no critical vulnerabilities
Muse is the first personal AI agent we're announcing support for. It won't be the last.
Personal AI Agents Are Here, and Aembit Customers Can Secure Them Today (2026-10-05)Source ↗
Oct 52026
updatedAembit MCP Identity Gateway integration for personal AI agents
With Microsoft 365, GitHub
Use the Aembit MCP Identity Gateway , or use the gateways you already run. We integrate with many of the most popular ones and will add more as you need them. Coverage across your services. From Microsoft 365 and GitHub to the custom services your teams built in-house, all under one policy model.
Personal AI Agents Are Here, and Aembit Customers Can Secure Them Today (2026-10-05)Source ↗
Vulnerability & code scanning 1
Identity & access 1
Cloud platforms & services 1
Source control & CI/CD 1
Other 3
Agent frameworks & SDKs 1
Operating systems 1
Other 2
Nothing first seen in this window. That doesn't mean Aembit shipped nothing, only that we found no record of it.
Changes per month New Updated Retired
2026-10
6
How we count
Read from 9 of 136 release notes and docs updates we hold for Aembit. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through Aembit's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
Show
Coverage in all entries
136 entries
No entries match these filters.
October 202612
September 202626
August 20269
July 20262
June 202611
May 20269
April 20264
March 20262
February 20262
January 20262
December 20251
October 20251
August 20253
July 20252
June 20253
May 20253
April 20255
March 20252
February 20253
December 20241
November 20241
October 20246
September 20243
August 20242
July 20242
June 20245
May 20242
April 20244
March 20243
January 20242
December 20231
November 20231
October 20231
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can
follow every release here.
 Aembit Launches Identity and Access Security Controls for Meta Muse (2026-10-05) · Oct 2026
· source
· release history
 Introducing the AI Agent Kill Switch: Instant Single-User Revocation (2026-10-29) · Oct 2026
· source
· release history
 Introducing MCP Tool Filtering: Fine-Grained, Least-Privilege Authorization for AI Agents (2026-10-15) · Oct 2026
· source
· release history
 Aembit Adds Workload Identity Federation Support for the Claude API (2026-08-05) · Aug 2026
· source
· release history
 Choose a badge style and copy the code →