SailPoint
New Capability: SailPoint Oracle Access Governance SaaS Connector (2026-10-12) commercialThe section your link pointed to isn't on SailPoint's page any more, so we've brought you to the top.
SailPoint is an identity governance and access management platform that automates user provisioning, access reviews, and compliance across enterprise systems.
<entry key="useSpendApiV41" value="true"/>

<!-- Updated customData mapping pattern -->
<entry key="orgUnit1" value="['urn:ietf:params:scim:schemas:extension:spend:2.0:User'].customData[*][?(@.id=='orgUnit1')].value"/>
File Transport: SMB
Host: fileserver.lab.test
Port: 445
Share Name: \\fileserver\identities
Kerberos Realm: LAB.TEST
Username: svc_sailpoint
Password: <encrypted secret>
Kerberos Configuration Directory: /opt/sailpoint/krb5/
IQService.exe -g --enable ScriptExecutor
IQService.exe -g --enable gMSAPasswordData
// ~/.cursor/mcp.json
{
  "mcpServers": {
    "sailpoint-access-requests": {
      "url": "https://mcp.api.cloud.sailpoint.com/latest/access-requests/mcp",
      "auth": {
        "CLIENT_ID": "your-client-id",
        "scopes": ["sp:scopes:all"]
      }
    }
  }
}
# Commercial environments — add to your outbound firewall allowlist:
va-docker.secure-api.infra.identitynow.com

# FedRAMP environments — add to your outbound firewall allowlist:
va-docker.secure-api.saas.sailpointfedramp.com
$__util.getIdentityDetailsByID($someIdentityId)
Summary
SailPoint is a commercial identity security platform that governs user access, entitlements, and non-human identitiesnon-human identitiesA non-human identity, an account or credential used by software or a device rather than a person. Service accounts, workload identities and automation tokens need their own permissions and lifecycle controls. across enterprise systems, delivered mainly as a SaaSSaaSSoftware delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally. product (Identity Security Cloud) with a self-hosted option (IdentityIQ) for on-premises data centers. It is aimed at IAMIAMIdentity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access. and compliance teams responsible for access certification, privileged access governance, and cloud entitlement management, rather than at individual developers. Its documentation describes coverage extending from core identity governance into adjacent areas like CIEM, data access security, and machine and AI agent identity, connecting to systems such as Databricks, CyberArk, BeyondTrust, and Delinea for discovery and provisioning. Recent work includes activation-based Just-In-Time privileged access, OAuth-based agent access requests through Cursor and Claude Desktop, and permission-path visualization for reviewers.
SailPoint is an identity governance and access management platform that automates user provisioning, access reviews, and compliance across enterprise systems.
How SailPoint helps
Which entitlements are standing access that should really be granted only when work begins?
flags eligible entitlements for activation-based access, letting a user request and activate them for a bounded duration that expires automatically instead of holding privileged access all the time
How did a given user actually end up with access to a sensitive resource?
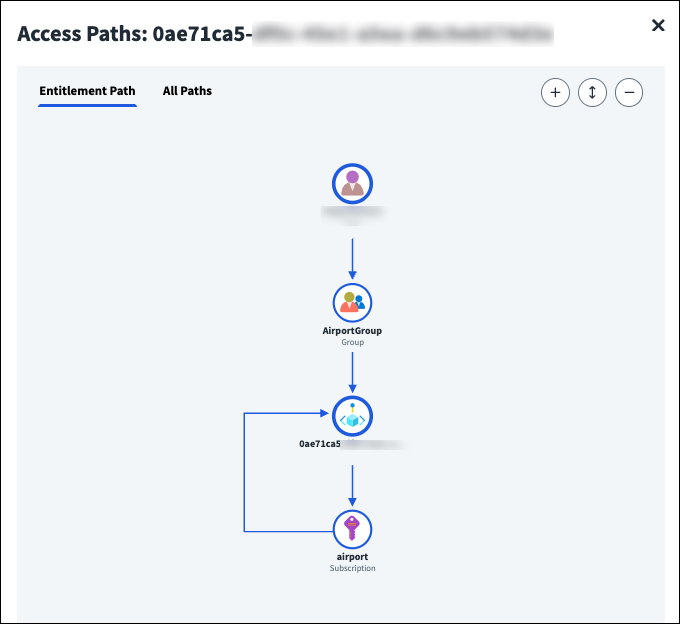
opens a permission path view from the certification screen showing the full chain that granted the access and whether it is actively used, including cases with multiple paths to the same resource
Which accounts in a Databricks deployment have more access than they need?
runs permission analysis against discovered Databricks Tables, Views, and Stored Procedures and surfaces over-permissioned accounts and entitlement sprawl
What privileged accounts and secrets exist across CyberArk, BeyondTrust, and Delinea that nobody has inventoried?
discovers managed systems and secrets through each vendor's API and maps them into datasets, now down to individual application instances for CyberArk rather than generic platform templates
Can an AI assistant like Cursor request and track access on a user's behalf without someone handing it a standing credential?
connects through a global OAuth 2.1 endpoint with browser login and consent, letting the assistant search the access catalog, submit and cancel requests, and check approval status conversationally with tokens refreshed automatically
Will a script that reads response headers from the API still work after an update?
notes that HTTP/2 enablement lowercases all header keys, so case-sensitive header matching in existing scripts breaks and needs updating
Languages
Features
Built from SailPoint's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- SailPoint covers 1 of the 2 secrets and credential hygiene capabilities we track.
What SailPoint offers you
- Administrative audit log4
- Web management console4
- REST API3
- Role-based access control3
- Scheduled jobs3
- Built-in AI assistant1
- CI/CD pipeline integration1
- Import from a competing product1
- MCP server1
- ML-based detection1
- Natural-language query1
- On-premises appliance1
- Single sign-on1
No capabilities match.
Multi-factor authentication 1 feature Identity and access since 2026
SaaS Application and Access Management (SAAM) discovery shipped Discovers SaaS applications and their risk signals via a browser extension and feeds them into access reviews, certifications, and app onboarding workflows.
Shared capability: Multi-factor authentication
release
- Supports Browser Extension (BE) connector in ISC for US-region customers, syncing SAAM discovery and risk data into ISC's Discovered Applications page with risk score, sensitivity, exposure, and credential/MFA signal columns. New Capability: US Region Deployment for SAAM (2026-07-27) · Jul 2026 · source · release history
- Adds AWS US East (us-east-1) region hosting for SAAM, giving US customers in-region data residency and lower latency. New Capability: US Region Deployment for SAAM (2026-07-27) · Jul 2026 · source · release history
- Enables the App Switcher Application Visibility portal in the US region for full SAAM configuration, discovery, risk & usage analytics, and privacy controls. New Capability: US Region Deployment for SAAM (2026-07-27) · Jul 2026 · source · release history
- Provides a direct discovery-to-governance path within ISC, enabling access reviews, certifications, and app onboarding without leaving the platform. New Capability: US Region Deployment for SAAM (2026-07-27) · Jul 2026 · source · release history
docs
- # SailPoint Application Visibility - [Microsoft Entra ID](idp/entra_idp.md) - [Okta](idp/okta_idp.md) - [Other IdP](idp/other_idp.md) Next, you must deploy the [browser extension](browser_extension/index.md) in your environment to discover user-related activities. !!! docs update · Oct 2026 · source
example
-
Set up the Browser Extension connector in ISC to surface US-region discovered apps with risk and exposure data on the Discovered Applications page.
In ISC, go to Admin > Connections > Discovery Connectors → Select Create Connector → choose Browser Extension category → Continue → Configure → Start Connector Setup → Run Discover to populate Admin…New Capability: US Region Deployment for SAAM (2026-07-27) · Jul 2026 · source
MCP server 1 feature Interfaces and integrations since 2026
Cursor IDE MCP integration shipped Adds native support for configuring the ISC MCP server inside Cursor IDE, handling the full OAuth authentication flow automatically on connection.
Shared capability: MCP server
Also counts toward: Single sign-on
release
-
Adds native Cursor IDE support: configure the global URL and Client ID in
~/.cursor/mcp.json, and the full OAuth flow is handled automatically on connect. Enhancement: SailPoint MCP Server Now Supports Global URL and OAuth — Connect Any AI Client in Minutes (2026-07-09) · Jul 2026 · source · release history -
New global MCP endpoint (
https://mcp.api.cloud.sailpoint.com/latest/access-requests/mcp) works for all non-FedRAMP tenants — no per-org URL construction needed. Enhancement: SailPoint MCP Server Now Supports Global URL and OAuth — Connect Any AI Client in Minutes (2026-07-09) · Jul 2026 · source · release history - Replaces manual PAT/token workflow with OAuth 2.1 + PKCE: browser-based login, SSO support, consent screen, and automatic token refresh for up to one month. Enhancement: SailPoint MCP Server Now Supports Global URL and OAuth — Connect Any AI Client in Minutes (2026-07-09) · Jul 2026 · source · release history
- Harbor Pilot is now available in Amazon sa-east-1 and us-gov-west-1 regions. SaaS Release Notes - June 12, 2026 · Jun 2026 · source · release history
- Harbor Pilot now shows reasoning process by revealing responses word by word instead of as a block of text. SaaS Release Notes - June 12, 2026 · Jun 2026 · source · release history
- Harbor Pilot has been approved for availability in FedRAMP environments. SaaS Release Notes - June 12, 2026 · Jun 2026 · source · release history
example
-
Create the required public OAuth API client in ISC before wiring up Cursor or Claude Desktop.
In the ISC console, go to Admin > Security Settings > API Management > Create API Client: - Set client type to Public - Enable Authorization Code + Refresh Token grants - Set Redirect URL to:…Enhancement: SailPoint MCP Server Now Supports Global URL and OAuth — Connect Any AI Client in Minutes (2026-07-09) · Jul 2026 · source -
Connect Cursor IDE to SailPoint ISC so an AI agent can handle access requests without manual token management.
// ~/.cursor/mcp.json { "mcpServers": { "sailpoint-access-requests": { "url": "https://mcp.api.cloud.sailpoint.com/latest/access-requests/mcp", "auth": { "CLIENT_ID": "your-client-id", "scopes":…Enhancement: SailPoint MCP Server Now Supports Global URL and OAuth — Connect Any AI Client in Minutes (2026-07-09) · Jul 2026 · source
Secrets management 1 feature Secrets and credential hygiene since 2026
Oracle Cloud Infrastructure Identity Connector shipped Adds an OCI IAM SaaS connector and expands aggregation to include token metadata, secrets, Vault metadata, identities, roles, and entitlements.
Shared capability: Secrets management
release
- Enables aggregation of token metadata (modeled as credentials) and userpass account metadata (modeled as machine accounts) without reading secret payloads. New Capability: HashiCorp Vault (On-Premise) Connector for NHI Discovery (2026-10-05) · Oct 2026 · source · release history
- Aggregates auth tokens, customer secret keys, SMTP credentials, and OCI Vault secret metadata in the Oracle Cloud Infrastructure SaaS connector's IAM Credentials and Vault Secrets datasets. SaaS Release Notes - September 25, 2026 · Sep 2026 · source · release history
-
Adds the
Oracle Access Governance SaaSconnector to Identity Security Cloud for aggregating identities, roles, entitlements, and supporting grants/revocations. SaaS Release Notes - September 25, 2026 · Sep 2026 · source · release history - Adds Oracle Cloud Infrastructure (OCI) IAM SaaS connector support for aggregating OCI IAM users as accounts, Generative AI Agents as machine identities, and API keys as credentials SaaS Release Notes - September 18, 2026 · Sep 2026 · source · release history
Other / not yet classified 85 features Features we have not matched to a capability yet. A suggested match is marked.
Identity graph UI shipped Displays identity and access relationships as an interactive graph with improved filtering, root-node highlighting, and searchable history so relationships are easy to explore.
release 21 total
- Allows ARM admins to edit a user's email address directly in the product, without contacting support. New Capability: SailPoint ARM brings Fiori Application IDs and utilization into SAP access risk (2026-10-09) · Oct 2026 · source · release history
- Adds quoted phrase search in the ISC Access Object Search widget: wrapping multi-word terms in double quotes in the Name, Description, or Additional Search fields matches a contiguous phrase (unquoted searches behave as in v5.3). Enhancement: ServiceNow Service Catalog v5.4 — Event-driven Approvals and Access Request Status Sync (2026-10-09) · Oct 2026 · source · release history
-
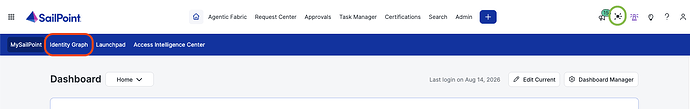
Accesses Identity Graph directly from the MySailPoint homepage and from context menus across the product by clicking the graph icon on any identity, entitlement, or access item.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
 New Availability: The SailPoint Identity Graph is Coming to Your Environment (2026-09-23) · Sep 2026
· source
· release history
- Visualizes agent-human relationships and flags overpermissioned identities by comparing access side-by-side. New Availability: The SailPoint Identity Graph is Coming to Business+ Tenants (2026-09-23) · Sep 2026 · source · release history
- Direct risk reduction actions can be taken from the Identity Graph interface without leaving the tool. New Availability: The SailPoint Identity Graph is Coming to Business+ Tenants (2026-09-23) · Sep 2026 · source · release history
- Identifies the blast radius of a compromised identity immediately, leveraging context across SailPoint's portfolio. New Availability: The SailPoint Identity Graph is Coming to Your Environment (2026-09-23) · Sep 2026 · source · release history
docs
- Identity Graph Graph visualization of a tenant's identity data and access model. seen Oct 2026 · source
example
-
Quickly view the blast radius of a compromised human or non-human identity directly from the homepage.
Click the red circle icon on the left side of the MySailPoint homepage to launch Identity Graph.New Availability: The SailPoint Identity Graph is Coming to Business+ Tenants (2026-09-23) · Sep 2026 · source -
Navigate to Identity Graph for a specific identity or entitlement directly from any list or menu in the product.
In any identity, entitlement, or access list across the SailPoint product, click the Identity Graph icon in the top right of the item row.New Availability: The SailPoint Identity Graph is Coming to Your Environment (2026-09-23) · Sep 2026 · source -
Navigate to Identity Graph from the MySailPoint homepage to immediately visualize a user's full access landscape and assess blast radius after a suspected compromise.
1. Log in to your MySailPoint homepage. 2. Click the Identity Graph icon (red circle on the left sidebar). 3. Search for the suspected compromised identity. 4.New Availability: The SailPoint Identity Graph is Coming to Business+ Tenants (2026-09-23) · Sep 2026 · source -
Investigate access pathways for a specific user or agent from within any list view.
Click the green circle icon appearing on an identity item in menus or lists to load its Identity Graph context.New Availability: The SailPoint Identity Graph is Coming to Business+ Tenants (2026-09-23) · Sep 2026 · source
AI agent and non-human identity (NHI) governance shipped Provides a unified registry, lifecycle controls, approval workflows, and threat monitoring for AI agents and non-human identities across endpoint, enterprise, and browser surfaces.
Also counts toward: Administrative audit log
release 18 total
- Enables activation and deactivation of Cursor agents via the Cursor SaaS connector SaaS Release Notes - August 28, 2026 · Aug 2026 · source · release history
-
Adds
JDBC SaaSconnector support for the Dataset Resource model to aggregate non-human identity (NHI) entities including Agents, MCP Servers, and Tools with agent owner correlation. SaaS Release Notes - August 21, 2026 · Aug 2026 · source · release history - Supports AWS IAM roles as governable machine accounts within SailPoint Agentic Fabric and Machine Identity Security SaaS Release Notes - August 14, 2026 · Aug 2026 · source · release history
- Adds SailPoint Agentic Fabric suite for discovering, governing, and auditing non-human identities (NHIs) and AI agents SaaS Release Notes - August 14, 2026 · Aug 2026 · source · release history
- Adds Multi Owner Correlation and Succession to automatically map human owners to machine identities and handle succession SaaS Release Notes - August 14, 2026 · Aug 2026 · source · release history
- Adds approval routing for agent provisioning (activation/deactivation) configurable under Global → System Settings → Approval Settings → Agent Requests. New Product: SailPoint Agentic Fabric (2026-07-22) · Jul 2026 · source · release history
docs
- # SailPoint Agentic Fabric SailPoint Agentic Fabric is an agent governance capability in SailPoint Human Fabric. docs update · Oct 2026 · source
- # Shadow AI Remediation Shadow AI Remediation provides real-time visibility and control over how AI tools are being used by employees, and just-in-time remediation through guided [playbooks](playbooks/index.md). - GenAI and AI orchestration web applications. - GenAI applications registered to the IdP. docs update · Oct 2026 · source
- After Agentic Fabric is activated, the non-human identity registry offers users a central place to view and manage their non-human identities. These include agents, applications, accounts, MCP clients, credentials, and endpoints. docs update · Aug 2026 · source
- SailPoint Agentic Fabric SailPoint Agentic Fabric is an agent governance capability in Identity Security Cloud. docs update · Aug 2026 · source
example
-
Navigate to agent approval routing to configure who must approve activation or deactivation of AI agents before provisioning proceeds.
In the ISC console, go to Global → System Settings → Approval Settings → Agent Requests and configure approval routing for agent provisioning operations.New Product: SailPoint Agentic Fabric (2026-07-22) · Jul 2026 · source -
Review all machine accounts and NHIs in one place to assess IAM role exposure across your environment.
In the ISC console, open the Agentic Fabric tab in the top navigation, then select Accounts from the left nav to view all machine accounts (IAM roles) and machine/application identities.New Product: SailPoint Agentic Fabric (2026-07-22) · Jul 2026 · source -
Monitor sensitive data pasting into GenAI apps by defining detection keywords.
Configure 'Shadow AI Remediation' in the Security Cloud console to define keywords and enable end-user guidance playbookSaaS Release Notes - June 19, 2026 · Jun 2026 · source
Quick Compliance Connectors shipped Provides prebuilt integration connectors for a wide range of SaaS and on-prem applications to rapidly establish compliance controls.
Also counts toward: CI/CD pipeline integration
release 18 total
- Adds the Oracle Access Governance (OAG) SaaS connector for SailPoint Identity Security, enabling centralized visibility, lifecycle management, access requests, and governance over OAG-managed identities and Oracle applications.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New Capability: SailPoint Oracle Access Governance SaaS Connector (2026-10-12) · Oct 2026 · source · release history
-
Certifies
SAP Sybase 16.1as a managed system for the SAP Sybase ASE connector. SaaS Release Notes - September 25, 2026 · Sep 2026 · source · release history -
Adds the
TeamCitySaaS connector for aggregating users as accounts, groups/roles as entitlements, and access tokens/SSH keys as non-human identities SaaS Release Notes - September 18, 2026 · Sep 2026 · source · release history - Adds Spacelift SaaS connector to Identity Security Cloud SaaS Release Notes - September 4, 2026 · Sep 2026 · source · release history
- Adds Bitbucket Cloud SaaS connector with NH visibility via deploy keys and pipeline variables SaaS Release Notes - September 4, 2026 · Sep 2026 · source · release history
-
Adds
CircleCISaaS connector with NH visibility via checkout, SSH, and deploy keys SaaS Release Notes - September 4, 2026 · Sep 2026 · source · release history
docs
- Checkmk Cloudiway Condens FOSSA Infisical Kashoo Nifty Qdrant Scrive StackHawk Trigger Vendasta YouSign docs update · Sep 2026 · source
- Absence.io Attio FreeAgent GitGuardian Holded Movidesk Ploomes ProdPad SOTI MobiControl StatusGator docs update · Sep 2026 · source
- AlertOps Bill4Time Canny Documo Honeybadger Huntress Kobiton Labelbox PactFlow Recruitee Scalefusion docs update · Sep 2026 · source
example
-
Use Quick Compliance to quickly set up aggregation for one of the new supported sources.
In the console, navigate to 'Quick Compliance' and select a source from the list (e.g., Checkmk, FOSSA, StackHawk).SaaS Release Notes - September 18, 2026 · Sep 2026 · source -
Configure a new vendor integration token with a specific vendor selected.
When creating a new API Token or Personal Access Token for an authorized vendor integration, select the vendor in the configuration process.SaaS Release Notes - August 7, 2026 · Aug 2026 · source
Workflow builder enhancements shipped Makes workflow POST response bodies inspectable during testing and trims outgoing payloads to only the fields actually used downstream, reducing stored data.
release 16 total
- Allows comparison between versions (including after a fork) directly from a version-oriented event in the History tab. Enhancement: Workflow Versioning — History tab (2026-09-24) · Sep 2026 · source · release history
- Enables following a version-oriented event to compare two workflow versions side-by-side, including across forks. Enhancement: Workflow Versioning — History tab (2026-09-24) · Sep 2026 · source · release history
- Enables version comparison from within the History tab, letting admins follow changes that spawned a version and open a diff, including after a fork. Enhancement: Workflow Versioning — History tab (2026-09-23) · Sep 2026 · source · release history
- Enables Activity Output Trimming for POST requests in the Workflows HTTP Request Action to reduce payload sizes when output feeds into a loop SaaS Release Notes - September 11, 2026 · Sep 2026 · source · release history
- Workflow uploads fail during the Staging-to-Production gap if the trigger filter uses the target environment's mismatched format Enhancement: A Guided Builder for Workflow Trigger Filters (2026-09-09) · Sep 2026 · source · release history
- Adds missing-filter warnings in the workflow editor and on the Test Workflow experience when a filterable trigger has no filter configured. Enhancement: Easier Trigger Filter Testing in Workflows (2026-08-31) · Aug 2026 · source · release history
example
-
Use the Basic mode filter builder in the Workflows UI to add a trigger filter without writing JSONPath, then verify it matches your test input before promoting.
In Identity Security Cloud, go to Workflows > select a workflow with a filterable event trigger > Trigger > Filter > switch to Basic mode > add conditions using AND/OR logic from the trigger schema >…Enhancement: A Guided Builder for Workflow Trigger Filters (2026-09-09) · Sep 2026 · source -
Set a future effective date for an approved access request using the new workflow field.
In the Workflows Manage Access action, select the 'Access Start Date' field to define when the approved access takes effect.SaaS Release Notes - June 26, 2026 · Jun 2026 · source -
Use the new operator to evaluate complex conditions without splitting logic across steps.
In Workflows builder, select 'Define Comparison' operator and choose Advanced JSON view to define criteriaSaaS Release Notes - June 19, 2026 · Jun 2026 · source -
Retrieve identity details within a V2 template using the new utility functions.
$__util.getIdentityDetailsByID($someIdentityId)SaaS Release Notes - May 15, 2026 · May 2026 · source
Just-in-Time Privileged Access (Privilege On Demand) shipped Grants eligible users time-limited privileged access that expires automatically, with self-service activation, approval workflows, and a full per-entitlement audit record.
Also counts toward: Administrative audit log
release 17 total
-
Adds Quick Compliance support for
AlertOps, Bill4Time, Canny, Documo, Honeybadger, Huntress, Kobiton, Labelbox,PactFlow, Recruitee, and Scalefusion connectors SaaS Release Notes - September 4, 2026 · Sep 2026 · source · release history - Expands Quick Compliance connectors to include Anypoint Exchange, Castor EDC, Doppler, Givebutter, IBM NS1 Connect, Kommo, Moneybird, and Runrun.it for expedited read-only account and entitlement aggregation. SaaS Release Notes - August 21, 2026 · Aug 2026 · source · release history
- Enables Just-In-Time (JIT) activation of approved entitlements via Privilege on Demand in Identity Security Cloud SaaS Release Notes - August 14, 2026 · Aug 2026 · source · release history
- Adds Privilege on Demand UI in Launchpad > Just-In-Time Access for users to activate time-bounded access SaaS Release Notes - August 14, 2026 · Aug 2026 · source · release history
- Admins can configure JIT behavior in System Settings > Feature Settings for Privilege on Demand SaaS Release Notes - August 14, 2026 · Aug 2026 · source · release history
- Introduces Privilege On Demand (JIT-P v1.0): an activation-based model where eligible entitlements are requested, then explicitly activated for a bounded duration with automatic expiration — replacing always-on standing access. New Capability: Privilege On Demand (2026-07-08) · Jul 2026 · source · release history
example
-
Monitor scheduled access revocations via audit logs after end date modifications.
Review the 'Access Request' audit logs for events related to end date changes.SaaS Release Notes - September 18, 2026 · Sep 2026 · source -
Configure JIT activation windows and mark entitlements as eligible so users can activate privileged access on demand rather than holding it standing.
In the Admin console, go to Admin Settings > Privilege on Demand and set global JIT activation duration and extension duration.New Capability: Privilege On Demand (2026-07-08) · Jul 2026 · source
AI-assisted Web Services connector configuration shipped Uses AI to guide administrators through configuring REST and SCIM connectors, recommending endpoints and attribute mappings with live data previews before anything is saved.
Also counts toward: REST API
release 17 total
-
Adds Public Key option to the Authentication Type dropdown when
File Transport = SFTP, enabling SSH private key configuration (PEM, OpenSSH, or OpenSSH v1 formats) for SFTP connections. Enhancement: Delimited File Connector - Beyond Basic Authentication - SSH Keys for SFTP and Client Certificates for FTPS (2026-09-04) · Sep 2026 · source · release history -
Adds Public Key option to the Authentication Type dropdown for SFTP (
File Transport = SFTP), enabling SSH private key authentication with SSH Private Key (PEM, OpenSSH, or OpenSSH v1 format) and optional SSH Private Key Passphrase fields. Enhancement: Delimited File Connector - Beyond Basic Authentication - SSH Keys for SFTP and Client Certificates for FTPS (2026-09-04) · Sep 2026 · source · release history -
Adds Client Certificate option to the Authentication Type dropdown for FTPS (
File Transport = FTPS), enabling TLS mutual auth via a Base64-encoded PKCS12 (.p12) certificate pasted into FTPS Client Certificate, with an optional FTPS Client Certificate Passphrase field. Enhancement: Delimited File Connector - Beyond Basic Authentication - SSH Keys for SFTP and Client Certificates for FTPS (2026-09-04) · Sep 2026 · source · release history -
Adds Client Certificate option to the Authentication Type dropdown when
File Transport = FTPS, enabling Base64-encoded PKCS12 (.p12) certificate and passphrase configuration for TLS layer authentication in FTPS. Enhancement: Delimited File Connector - Beyond Basic Authentication - SSH Keys for SFTP and Client Certificates for FTPS (2026-09-04) · Sep 2026 · source · release history - Test Connection now validates SSH key authentication (invalid keys, wrong passphrases, network errors) and FTPS TLS handshake and FTP login before aggregation is scheduled. Enhancement: Delimited File Connector - Beyond Basic Authentication - SSH Keys for SFTP and Client Certificates for FTPS (2026-09-04) · Sep 2026 · source · release history
- Adds Client Credentials grant type support to Generic SDIM connector for OAuth 2.0 authentication SaaS Release Notes - August 28, 2026 · Aug 2026 · source · release history
Access Risk Management shipped Extracts and ingests SAP Security Audit Log data for compliance and risk analysis.
release 12 total
- Adds a new Fiori report listing which roles and catalogs grant which Fiori apps and OData services, with or without usage, filterable by Fiori Application ID as a dedicated field. New Capability: SailPoint ARM brings Fiori Application IDs and utilization into SAP access risk (2026-10-09) · Oct 2026 · source · release history
- Adds a new out-of-the-box (OOTB) connector to manage Access Risk Management users' JML (Joiner-Mover-Leaver) access through ISC. New Capability: SailPoint ARM brings Fiori Application IDs and utilization into SAP access risk (2026-10-09) · Oct 2026 · source · release history
-
Surfaces Fiori intents and OData services in the emergency access activity grid, each row showing a readable description (e.g.
(F2223) Reset Cleared Items), a sensitivity flag, and a Standard or Elevated access marker. New Capability: SailPoint ARM brings Fiori Application IDs and utilization into SAP access risk (2026-10-09) · Oct 2026 · source · release history -
Existing rulebook entries for Fiori that lack a prefix must be updated: Fiori intents now require the
[FAPP]prefix and OData services require the[SVC]prefix before the next rulebook import, or they will not match correctly. New Capability: SailPoint ARM brings Fiori Application IDs and utilization into SAP access risk (2026-10-09) · Oct 2026 · source · release history -
Supports Fiori intents with the
[FAPP]prefix and OData services with the[SVC]prefix in rulebook risk definitions, alongside existing transaction codes. New Capability: SailPoint ARM brings Fiori Application IDs and utilization into SAP access risk (2026-10-09) · Oct 2026 · source · release history - Lets administrators choose whether to continue collecting raw OData service calls from the SAP Security Audit Log independently of app-level Fiori usage. New Capability: SailPoint ARM brings Fiori Application IDs and utilization into SAP access risk (2026-10-09) · Oct 2026 · source · release history
example
-
During an emergency access review, inspect exactly which Fiori apps an elevated user opened — with plain-language names, sensitivity flags, and Standard vs. Elevated markers.
In ARM, open an emergency access review for the target session and check the activity grid — Fiori rows appear alongside transactions, each labeled with its Application ID and description (e.g.New Capability: SailPoint ARM brings Fiori Application IDs and utilization into SAP access risk (2026-10-09) · Oct 2026 · source -
View executive risk posture and drill into role or user risk details.
Access the new Analysis Dashboard in Access Risk Management to view summary by severity, execution status, aging, risk type, and business process.SaaS Release Notes - August 7, 2026 · Aug 2026 · source
Personal Access Token lifecycle management shipped Gives admins a central screen to view, edit, and revoke Personal Access Tokens across the organisation, and enforces expiration on all tokens including legacy ones.
Also counts toward: Web management console
release 10 total
- Adds vendor selection capability when creating API Tokens or Personal Access Tokens for authorized vendor integrations SaaS Release Notes - August 7, 2026 · Aug 2026 · source · release history
-
Adds
Admin > Security Settings > Personal Access Tokenspage to view and edit expiration dates for organization-wide Personal Access Tokens SaaS Release Notes - July 31, 2026 · Jul 2026 · source · release history - Any Personal Access Token created before February 5, 2026 that has never had an expiration date added or removed will automatically be assigned an expiration date 6 months (180 days) from the release date (production rollout: 7/28/2026), which may break long-lived integrations relying on those tokens remaining… New Capability: Personal Access Token Management for Admins (2026-07-20) · Jul 2026 · source · release history
- Admins can change or remove expiration dates on any PAT across the organization. New Capability: Personal Access Token Management for Admins (2026-07-20) · Jul 2026 · source · release history
- Requires admins to select an approved integration when creating API or Personal Access Tokens, enabling per-integration traffic visibility. Enhancement: Support for Stronger Integrations (2026-07-20) · Jul 2026 · source · release history
- New Bulk update PAT expiration API enables programmatic management of PAT expiration dates at scale. New Capability: Personal Access Token Management for Admins (2026-07-20) · Jul 2026 · source · release history
example
-
Review all organization-wide Personal Access Tokens and modify their expiration dates directly from the new UI page.
Navigate to Admin > Security Settings > Personal Access TokensSaaS Release Notes - July 31, 2026 · Jul 2026 · source -
Audit and revoke stale PATs across your org before they become a security risk — reach this without contacting individual users.
In the Admin console, go to Admin → Security Settings → Personal Access Tokens to view all tokens in the environment, then select one or more tokens and edit their expiration dates in bulk.New Capability: Personal Access Token Management for Admins (2026-07-20) · Jul 2026 · source -
Configure personal-access-token authentication
sail set pat
Catalog item request questionnaires shipped Collects additional context from requesters via questionnaires at the point of submitting an access request.
release 12 total
- Enables audit events for changes to access request end dates in Identity Security Cloud - Access Requests SaaS Release Notes - September 18, 2026 · Sep 2026 · source · release history
-
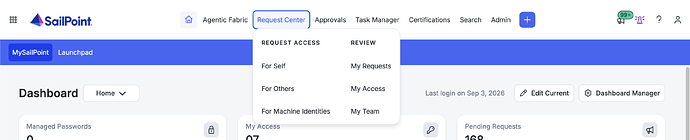
Introduces Next-Gen Access Request, replacing the legacy Request Center with a unified flow for requesting access for self, others, a team, or machine identities.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
 New Capability: Next-Gen Access Request (2026-09-08) · Sep 2026
· source
· release history
- Unified request flow for yourself, others, and teams with identity search by name, email, or manager; up to five public identity attribute filters; All/'My Team' toggle; and multiple identity selection New Capability: Next-Gen Access Request (2026-09-08) · Sep 2026 · source · release history
- Adds ability to attach forms to roles, access profiles, and entitlements in Access Requests to gather additional information from users requesting access. SaaS Release Notes - August 21, 2026 · Aug 2026 · source · release history
- Supports external access request portals (e.g., SailPoint ServiceNow Catalog Integration) by allowing supplementary form data to be passed into the request flow independent of the native UI. New Capability: Forms for Access Request (2026-07-24) · Jul 2026 · source · release history
- Makes form data accessible throughout the request flow, including before-provisioning rules, enabling custom provisioning logic driven by requester-supplied data. New Capability: Forms for Access Request (2026-07-24) · Jul 2026 · source · release history
PAM discovery connectors shipped Discovers secrets and privileged accounts from Delinea Secret Server and CyberArk Privilege Cloud so they can be governed alongside other identities.
release 10 total
- Adds Delinea Platform SaaS connector support in Identity Security Connectivity SaaS Release Notes - September 18, 2026 · Sep 2026 · source · release history
- Adds Buildkite SaaS connector to aggregate organization members as accounts, organization roles and teams as entitlements, agent tokens, secrets, and registry tokens as non-human identities SaaS Release Notes - September 11, 2026 · Sep 2026 · source · release history
- Adds Octopus Deploy SaaS connector to aggregate users as accounts, teams and user roles as entitlements, service accounts, API keys, and stored credentials as non-human identities SaaS Release Notes - September 11, 2026 · Sep 2026 · source · release history
- New Delinea Secret Server PAM Discovery connector discovers secrets and associated metadata (names, IDs, template types, creation dates, active status) from Delinea Secret Server via OAuth 2.0, mapping results into ISC-consumable datasets. Expanding PAM application discovery: CyberArk Enhancement and New BeyondTrust & Delinea connectors (2026-07-09) · Jul 2026 · source · release history
- Upgrades CyberArk Privilege Cloud Shared Services PAM Discovery connector to discover individual application instances (e.g., three MySQL instances as three distinct entries) rather than generic platform templates. Expanding PAM application discovery: CyberArk Enhancement and New BeyondTrust & Delinea connectors (2026-07-09) · Jul 2026 · source · release history
- Breaking change for existing CyberArk Discovery customers: next discovery aggregation after the update will return instance-level applications instead of platform templates; new Safe-level read permissions must be configured on the CyberArk service user before the next scheduled run or discovery may return no results. Expanding PAM application discovery: CyberArk Enhancement and New BeyondTrust & Delinea connectors (2026-07-09) · Jul 2026 · source · release history
example
-
Set up the new Delinea Secret Server PAM Discovery connector to catalogue secrets and their metadata in ISC.
In the ISC console, go to Admin > Connections > Discovery Connectors > Create Connector > PAM category > Configure next to "Delinea Secret Server PAM".Expanding PAM application discovery: CyberArk Enhancement and New BeyondTrust & Delinea connectors (2026-07-09) · Jul 2026 · source -
Validate the upgraded CyberArk connector returns instance-level results after granting Safe-level permissions to avoid a blank discovery run.
In Privilege Cloud, go to Policies > Safes, open each relevant Safe > Members > Add Member, add the connector service user with Read-only + Access enabled permissions.Expanding PAM application discovery: CyberArk Enhancement and New BeyondTrust & Delinea connectors (2026-07-09) · Jul 2026 · source
File transport authentication enhancements shipped Adds support for Public Key (SSH) and Client Certificate (FTPS/TLS mutual auth) authentication options for file-based connectors, with encrypted storage of keys and passphrases.
release 8 total
- Introduces Kerberos Configuration Directory setting in source configuration to specify a persistent path for krb5.conf Enhancement: Delimited File Connector - SMB File Transport with Kerberos Authentication (2026-10-05) · Oct 2026 · source · release history
-
Adds Public Key option to the Authentication Type dropdown when
File Transport = SFTP, enabling SSH private key configuration (PEM, OpenSSH, or OpenSSH v1 formats) for SFTP connections. Enhancement: Delimited File Connector - Beyond Basic Authentication - SSH Keys for SFTP and Client Certificates for FTPS (2026-09-04) · Sep 2026 · source · release history -
Adds Public Key option to the Authentication Type dropdown for SFTP (
File Transport = SFTP), enabling SSH private key authentication with SSH Private Key (PEM, OpenSSH, or OpenSSH v1 format) and optional SSH Private Key Passphrase fields. Enhancement: Delimited File Connector - Beyond Basic Authentication - SSH Keys for SFTP and Client Certificates for FTPS (2026-09-04) · Sep 2026 · source · release history -
Adds Client Certificate option to the Authentication Type dropdown for FTPS (
File Transport = FTPS), enabling TLS mutual auth via a Base64-encoded PKCS12 (.p12) certificate pasted into FTPS Client Certificate, with an optional FTPS Client Certificate Passphrase field. Enhancement: Delimited File Connector - Beyond Basic Authentication - SSH Keys for SFTP and Client Certificates for FTPS (2026-09-04) · Sep 2026 · source · release history -
Adds Client Certificate option to the Authentication Type dropdown when
File Transport = FTPS, enabling Base64-encoded PKCS12 (.p12) certificate and passphrase configuration for TLS layer authentication in FTPS. Enhancement: Delimited File Connector - Beyond Basic Authentication - SSH Keys for SFTP and Client Certificates for FTPS (2026-09-04) · Sep 2026 · source · release history - SSH private keys, client certificates, and passphrases are stored as encrypted attributes in Identity Security Cloud source configuration — no key files need to be uploaded to the Virtual Appliance filesystem. Enhancement: Delimited File Connector - Beyond Basic Authentication - SSH Keys for SFTP and Client Certificates for FTPS (2026-09-04) · Sep 2026 · source · release history
example
-
Connect to a hardened SFTP server requiring SSH key auth instead of passwords.
Select 'Public Key' in the Authentication Type dropdown (File Transport = SFTP) and paste your private key content.Enhancement: Delimited File Connector - Beyond Basic Authentication - SSH Keys for SFTP and Client Certificates for FTPS (2026-09-04) · Sep 2026 · source -
Authenticate to an FTPS server using a client certificate for TLS security.
Select 'Client Certificate' in the Authentication Type dropdown (File Transport = FTPS) and paste the Base64-encoded .p12 content.Enhancement: Delimited File Connector - Beyond Basic Authentication - SSH Keys for SFTP and Client Certificates for FTPS (2026-09-04) · Sep 2026 · source -
Configure a Delimited File source to authenticate to a hardened SFTP server using an SSH private key instead of a password.
In the Identity Security Cloud admin console, open the Delimited File source > Connection Settings. Set 'File Transport' to SFTP, then set 'Authentication Type' to 'Public Key'.Enhancement: Delimited File Connector - Beyond Basic Authentication - SSH Keys for SFTP and Client Certificates for FTPS (2026-09-04) · Sep 2026 · source
Non-human identity and AI agent connector support shipped Extends the platform to discover and aggregate data from specific non-human identities, including Snowflake Cortex Agents, Databricks Mosaic AI Agents, GitHub Copilot/Workflows, Microsoft Entra Managed Identities, and Claude Enterprise.
Also counts toward: MCP server
release 11 total
- Adds discovery of Amazon Quick agents and action connectors with permission-grant relationships in the AWS SaaS connector. SaaS Release Notes - September 25, 2026 · Sep 2026 · source · release history
-
Adds
N8Nconnectivity support for account entitlement aggregation and NHI visibility SaaS Release Notes - September 4, 2026 · Sep 2026 · source · release history - Enables activation and deactivation of N8N agents via the N8N SaaS connector SaaS Release Notes - August 28, 2026 · Aug 2026 · source · release history
-
Adds
Snowflake SaaSconnector support for the Dataset resource model for Snowflake Cortex Agents, aggregating capabilities like Cortex Analyst, Cortex Search, generic functions/procedures, MCP servers, skills, web search, data-to-chart, and code execution. SaaS Release Notes - August 21, 2026 · Aug 2026 · source · release history -
Adds
Databricks SaaSconnector support for the Dataset resource model for Databricks Mosaic AI Agents, allowing activation/deactivation of agents as dedicated agent resources with agent owner correlation. SaaS Release Notes - August 21, 2026 · Aug 2026 · source · release history -
Adds
GitHub SaaSconnector support for aggregating fine-grained tokens, personal access tokens, GitHub Copilot agents, GitHub Workflows, and GitHub environments as datasets. SaaS Release Notes - August 21, 2026 · Aug 2026 · source · release history
Workflow Trigger Filter Builders shipped Provides Basic mode (guided condition builder) and retains Advanced mode (JSONPath) for authoring workflow trigger filters.
release
- Existing workflows now present trigger filters in the new format via View, Edit, Download, and List actions Enhancement: A Guided Builder for Workflow Trigger Filters (2026-09-09) · Sep 2026 · source · release history
- View, Edit, Download, and List operations now present trigger filters in the new trigger filter format after this update is enabled. Enhancement: A Guided Builder for Workflow Trigger Filters (2026-09-09) · Sep 2026 · source · release history
- Adds a Basic mode guided condition builder for workflow trigger filters, using AND/OR logic derived from the trigger schema, as an alternative to writing JSONPath expressions.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enhancement: A Guided Builder for Workflow Trigger Filters (2026-09-09) · Sep 2026 · source · release history
- Adds a Basic mode in the Workflows UI that lets Org Admins build trigger filters using conditions from the trigger schema with AND / OR logic, without writing JSONPath Enhancement: A Guided Builder for Workflow Trigger Filters (2026-09-09) · Sep 2026 · source · release history
-
Adds
Improved filter testing: Your trigger filter is applied during test against the test input, so you can see whether the filter matchesEnhancement: Easier Trigger Filter Testing in Workflows (2026-08-31) · Aug 2026 · source · release history - Adds trigger filter recommendations and warning icons for filterable workflow triggers in Identity Security Cloud Workflows SaaS Release Notes - August 7, 2026 · Aug 2026 · source · release history
docs
- Anvil Checkmk Cloudiway Condens DataHub Employment Hero FOSSA Freshcaller Infisical Juniper Mist Kashoo LangChain Nifty noCRM Qdrant Redpanda Cloud Control Plane Scrive StackHawk Trigger Vendasta YouSign docs update · Sep 2026 · source
example
-
Use the Basic mode filter builder in the Workflows UI to add a trigger filter without writing JSONPath, then verify it matches your test input before promoting.
In Identity Security Cloud, go to Workflows > select a workflow with a filterable event trigger > Trigger > Filter > switch to Basic mode > add conditions using AND/OR logic from the trigger schema >…Enhancement: A Guided Builder for Workflow Trigger Filters (2026-09-09) · Sep 2026 · source -
Build a new trigger filter using the UI without knowing JSONPath syntax.
Steps: In Workflows, edit a workflow, click 'Trigger', select 'Basic' mode from the builder dropdown, choose conditions from the trigger schema (e.g., attribute = value), combine them with AND/OR,…Enhancement: A Guided Builder for Workflow Trigger Filters (2026-09-09) · Sep 2026 · source -
Handle the staging/production gap by stripping filters before upload.
Steps: In your JSON workflow definition, delete the `trigger.filter` field entirely. Upload the file to the target environment (Staging or Production).Enhancement: A Guided Builder for Workflow Trigger Filters (2026-09-09) · Sep 2026 · source -
Validate a JSONPath trigger filter against a real test payload before enabling a workflow, to confirm only intended events will fire it.
In Identity Security Cloud, open your Workflow > select a filterable event trigger > add your JSONPath filter expression > go to 'Test Workflow', provide your test input JSON, and run the test.Enhancement: Easier Trigger Filter Testing in Workflows (2026-08-31) · Aug 2026 · source
Non-Employee Risk Management (NERM) ISC sync and role management shipped Keeps non-employee identities and their roles in sync with Identity Security Cloud in real time, and lets admins manage those role assignments directly from the UI.
Also counts toward: Web management console
release 8 total
- Report creators can now delete their own report definitions directly from the Reports page in Non-Employee Risk Management; deleting a report also removes all associated exports. New Capability: Non-Employee Risk Management Report Delete & Visibility (2026-08-10) · Aug 2026 · source · release history
- The Reports All tab now shows only reports the logged-in user created or reports shared with them, preventing exposure of sensitive metadata in report titles to unauthorized users. New Capability: Non-Employee Risk Management Report Delete & Visibility (2026-08-10) · Aug 2026 · source · release history
- Allows Non-Employee Risk Management API requests to be authenticated with Identity Security Cloud API keys in addition to Personal Access Tokens SaaS Release Notes - August 7, 2026 · Aug 2026 · source · release history
- Adds support for OAuth credentials as an authentication method in Non-Employee Risk Management user and profile sources SaaS Release Notes - July 31, 2026 · Jul 2026 · source · release history
- Enables automatic synchronization for Non-Employee Risk Management user accounts and roles without scheduled aggregations SaaS Release Notes - July 17, 2026 · Jul 2026 · source · release history
- Adds a new Sync with Identity Security Cloud toggle in Admin > System > Identity Security Cloud Connection Settings > USERS tab, triggering immediate account or entitlement aggregation on any NERM user/role change instead of waiting for periodic aggregation. Enhancement: Non-Employee Risk Management Users Connector - Automatic Synchronization (2026-07-14) · Jul 2026 · source · release history
docs
- # SailPoint Non-Employee Risk Management Admin Help !!! important Non-Employee Risk Management can be used as an authoritative source for your organization's non-employee identity governance information, but it should not be the sole repository. seen Oct 2026 · source
example
-
Assign a role to a non-employee user directly in the UI during implementation, without needing API access.
In the NERM Admin UI, go to Admin > Lifecycle > User Roles, select the target user, and assign or unassign the desired role.Enhancement: Non-Employee Risk Management Users Connector - Automatic Synchronization (2026-07-14) · Jul 2026 · source -
Enable real-time ISC sync so that every NERM user or role change immediately triggers an aggregation in Identity Security Cloud, eliminating propagation delay.
In the NERM Admin UI, go to Admin > System > Identity Security Cloud Connection Settings > USERS tab, set the 'Sync with Identity Security Cloud' toggle to ON, confirm or enter the Source ID, then…Enhancement: Non-Employee Risk Management Users Connector - Automatic Synchronization (2026-07-14) · Jul 2026 · source
ISC navigation redesign shipped Reorganises the ISC header navigation to centre core items and the Admin megamenu, giving a consistent layout across ISC and Data Access Security.
release 10 total
- Delivers a side and top navigation overhaul for customers not on legacy reporting. New Capability: SailPoint ARM brings Fiori Application IDs and utilization into SAP access risk (2026-10-09) · Oct 2026 · source · release history
-
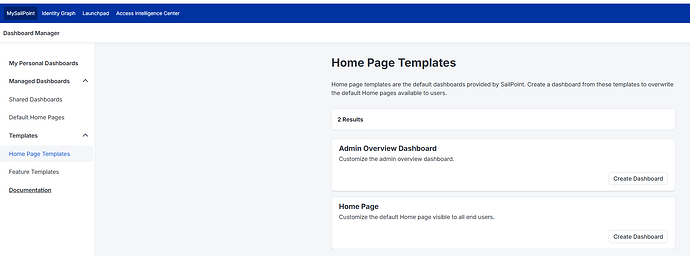
Adds a Default Home Pages section under Managed Dashboards > Default Home Pages where published managed defaults can be further edited or deleted (deleting reverts to the SailPoint baseline).
 Enhancement: MySailPoint Managed Defaults, Dashboard Templates & Widget Sizing (2026-08-19) · Aug 2026
· source
· release history
- Adds instance badge configuration in Admin > System Settings > Product Branding to indicate environment context SaaS Release Notes - August 14, 2026 · Aug 2026 · source · release history
- Moves the Admin tab and its megamenu to the top center of the screen for a symmetrical, at-a-glance view of all menu and submenu items. Enhancement: Centered Navigation Bar for Enhanced User Experience (2026-07-24) · Jul 2026 · source · release history
- Centers core navigation items (home icon, primary product tabs) in the header for end users to reduce eye and mouse fatigue. Enhancement: Centered Navigation Bar for Enhanced User Experience (2026-07-24) · Jul 2026 · source · release history
- Applies the same centered navigation layout to Data Access Security, creating a consistent visual experience when switching between ISC and DAS. Enhancement: Centered Navigation Bar for Enhanced User Experience (2026-07-24) · Jul 2026 · source · release history
Dashboard management and customization shipped Provides pre-built Dashboard Templates, multi-size widget support, Managed Defaults for global home layouts, and an Admin Overview template to configure and control the user dashboard experience.
release 8 total
-
Access via
MySailPointhomepage icon or inline icons in menus/lists to load context for specific items.
New Availability: The SailPoint Identity Graph is Coming to Business+ Tenants (2026-09-23) · Sep 2026
· source
· release history
-
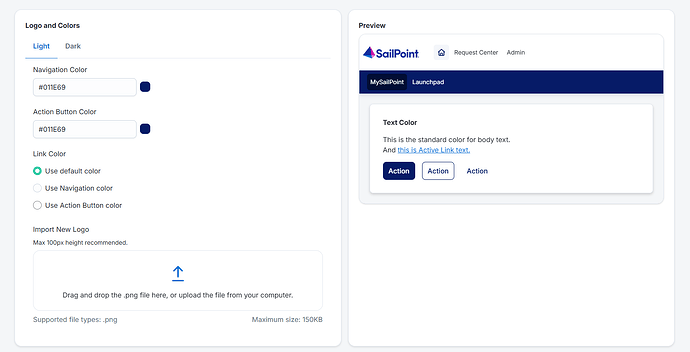
Adds color pickers for branding configuration.
 Enhancement: Dark Mode Updates (2026-09-09) · Sep 2026
· source
· release history
- Allows configuring default widgets and tiles on the MySailPoint Home Page using dashboard templates SaaS Release Notes - August 28, 2026 · Aug 2026 · source · release history
-
Adds Dashboard Templates: ready-made copyable dashboards covering persona, industry, or information type so admins can start with a pre-built layout instead of a blank canvas.
Enhancement: MySailPoint Managed Defaults, Dashboard Templates & Widget Sizing (2026-08-19) · Aug 2026
· source
· release history
- Adds multi-size widget support: widgets built by SailPoint product teams now ship as Small (three per row), Medium (two per row — current default), or Large (one per row); size is set at widget creation and is not configurable by admins. Enhancement: MySailPoint Managed Defaults, Dashboard Templates & Widget Sizing (2026-08-19) · Aug 2026 · source · release history
- Adds an Admin Overview dashboard template available by default to all administrators regardless of license, recreating the classic Admin Overview page's capabilities inside Custom Dashboards. Enhancement: MySailPoint Managed Defaults, Dashboard Templates & Widget Sizing (2026-08-19) · Aug 2026 · source · release history
example
-
Set an org-wide Home baseline so all users start from an approved layout when they first log in.
In the Dashboard Manager, go to Templates > Home Page Templates. Select 'Home Page', click 'Create Dashboard' to preview the default layout.Enhancement: MySailPoint Managed Defaults, Dashboard Templates & Widget Sizing (2026-08-19) · Aug 2026 · source -
Give your admin team an Admin Overview dashboard so they are ready before the classic Admin Overview page is deprecated.
In the Dashboard Manager, go to Templates > Home Page Templates. Select the 'Admin Overview' template and click 'Create Dashboard' to generate a copy.Enhancement: MySailPoint Managed Defaults, Dashboard Templates & Widget Sizing (2026-08-19) · Aug 2026 · source
Delimited File Connector IAM role authentication for S3 shipped Adds IAM Role as an authentication option for the Delimited File Connector when using AWS S3 transport, supporting cross-account bucket access, encrypted External ID storage, automatic credential refresh during long aggregation runs, and Test Connection validation with specific error messages.
release 8 total
- Adds IAM Role as an Authentication Type option in the Delimited File Connector source configuration to authenticate with AWS S3 without long-lived access keys. Enhancement: Delimited File Connector - Securely Connect to AWS S3 Using IAM Role Authentication Instead of Long-Lived Access Keys (2026-10-05) · Oct 2026 · source · release history
- Credentials refresh automatically throughout long aggregation runs, so a session is never limited to a single role-assumption window. Enhancement: Delimited File Connector - Securely Connect to AWS S3 Using IAM Role Authentication Instead of Long-Lived Access Keys (2026-10-05) · Oct 2026 · source · release history
- Extends Test Connection to validate IAM role access against the configured bucket/path and return specific success or failure messages for trust-policy, permission, and missing instance-profile errors. Enhancement: Delimited File Connector - Securely Connect to AWS S3 Using IAM Role Authentication Instead of Long-Lived Access Keys (2026-10-05) · Oct 2026 · source · release history
-
Stores External ID as an encrypted secret in Identity Security Cloud source configuration when the target role's trust policy includes an
sts:ExternalIdcondition. Enhancement: Delimited File Connector - Securely Connect to AWS S3 Using IAM Role Authentication Instead of Long-Lived Access Keys (2026-10-05) · Oct 2026 · source · release history -
Adds Authentication Type dropdown (values: IAM User or IAM Role) to the Delimited File Connector when
File Transport = AWS S3, letting practitioners choose IAM role auth instead of static access keys.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enhancement: Delimited File Connector - Securely Connect to AWS S3 Using IAM Role Authentication Instead of Long-Lived Access Keys (2026-10-05) · Oct 2026 · source · release history - Enables cross-account S3 bucket access by populating the optional 12-digit Account ID field when the target role lives in a different AWS account than the Virtual Appliance. Enhancement: Delimited File Connector - Securely Connect to AWS S3 Using IAM Role Authentication Instead of Long-Lived Access Keys (2026-10-05) · Oct 2026 · source · release history
example
-
Configure an AWS EC2-hosted VA Delimited File source to authenticate via a dedicated cross-account IAM role, avoiding any stored access keys.
In Identity Security Cloud, open your Delimited File source > Connection Settings. Set File Transport to `AWS S3`, then set Authentication Type to `IAM Role`.Enhancement: Delimited File Connector - Securely Connect to AWS S3 Using IAM Role Authentication Instead of Long-Lived Access Keys (2026-10-05) · Oct 2026 · source
Cloud Infrastructure Entitlement Management (CIEM) shipped Surfaces cloud resource tags and labels from AWS, Azure, and GCP within entitlement management views so access reviews can be scoped by tag or label.
release
- Adds tag/label-based search capability in SailPoint CIEM to query AWS/Azure tags and GCP labels for cloud resources SaaS Release Notes - August 28, 2026 · Aug 2026 · source · release history
- Enables CIEM ingestion of effective access and access paths for GCP AI Platform (Vertex/Gemini AI Agents) and Microsoft Cognitive Services (Foundry Agents) SaaS Release Notes - July 31, 2026 · Jul 2026 · source · release history
- Surfaces cloud resource tags and labels within CIEM AIC dashboards for reporting and governance validation across cloud environments. Enhancement: CIEM — Support for Cloud Resource Tags/Labels (2026-06-23) · Jun 2026 · source · release history
- Enables ISC Search to query cloud resources by tag/label key and value, supporting ad-hoc access reviews such as 'who can access PII-tagged resources'. Enhancement: CIEM — Support for Cloud Resource Tags/Labels (2026-06-23) · Jun 2026 · source · release history
- Adds native AWS Tags, Azure Tags, and GCP Labels visibility directly within the CIEM effective access view, enabling practitioners to see which identities can access tag-scoped resources. Enhancement: CIEM — Support for Cloud Resource Tags/Labels (2026-06-23) · Jun 2026 · source · release history
docs
-
# SailPoint CIEM Overview To get started, you must configure your cloud service providers and connect them to SailPoint Human Fabric. You will then manage the cloud entitlements within SailPoint Human Fabric.
 docs update · Oct 2026
· source
example
-
Locate cloud resources by their native tags in SailPoint CIEM.
Use Search interface to query AWS/Azure tags or GCP labelsSaaS Release Notes - August 28, 2026 · Aug 2026 · source -
When you need to answer 'who has access to production-tagged cloud resources', use ISC Search to filter by tag key and value without leaving SailPoint CIEM.
In ISC CIEM, go to Search and query by cloud resource tag key (e.g., Environment) and tag value (e.g., Production) to list all identities with effective access to matching resources.Enhancement: CIEM — Support for Cloud Resource Tags/Labels (2026-06-23) · Jun 2026 · source -
Run a search query against tenant events
sail search query "(type:provisioning AND created:[now-90d TO now])" --indices events
Dark Mode shipped Lets users switch to Dark Mode across SailPoint Agentic Fabric and select ISC pages.
release 8 total
- Expands dark mode support to more areas across Identity Security Cloud, including custom branding. SaaS Release Notes - September 25, 2026 · Sep 2026 · source · release history
-
Supports custom brand colors in Dark Mode, automatically switching between Light and Dark modes based on existing brand configuration.
Enhancement: Dark Mode Updates (2026-09-09) · Sep 2026
· source
· release history
- Extends Dark Mode support from Identity Security Cloud to Data Access Security (DAS) for a unified visual experience Enhancement: Dark Mode Updates (2026-09-09) · Sep 2026 · source · release history
- Extends Dark Mode configured in ISC automatically to Data Access Security (DAS) with no additional configuration required. Enhancement: Dark Mode Updates (2026-09-09) · Sep 2026 · source · release history
- Enables Dark Mode across Identity Security Cloud, including SailPoint Agentic Fabric and most ISC modules.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enhancement: Dark Mode Updates (2026-09-09) · Sep 2026 · source · release history
- Supports dark mode across SailPoint Agentic Fabric and limited support in Identity Security Cloud via user menu SaaS Release Notes - August 14, 2026 · Aug 2026 · source · release history
example
-
Ensure consistent dark theme across identity and data access modules after tenant configuration
In the ISC tenant, enable Dark Mode; it automatically extends to DAS.Enhancement: Dark Mode Updates (2026-09-09) · Sep 2026 · source
Machine Identity access request management shipped Lets users request access on behalf of machine identities and routes approvals to the correct owner automatically.
release 7 total
-
Adds dedicated machine identity request support for customers with the Machine Identity Security add-on, including filtering by owner or type.
New Capability: Next-Gen Access Request (2026-09-08) · Sep 2026
· source
· release history
- Machine identity access requests in a dedicated experience filtering by owner or type (requires Machine Identity Security add-on) New Capability: Next-Gen Access Request (2026-09-08) · Sep 2026 · source · release history
- Requires requesters to select a target account when a Machine Identity has multiple accounts on a source, ensuring precise provisioning targeting. New Capability: Machine Identity Access Requests (2026-08-10) · Aug 2026 · source · release history
- Routes manager-assigned approvals for Machine Identity access requests to the Machine Identity owner instead of a human manager. New Capability: Machine Identity Access Requests (2026-08-10) · Aug 2026 · source · release history
- Enables users to request entitlements on behalf of Machine Identities through the Identity Security Cloud (ISC) Request Center for Machine Identity Security customers. New Capability: Machine Identity Access Requests (2026-08-10) · Aug 2026 · source · release history
- Adds OAuth 2.1 with PKCE support to the SailPoint MCP Server for Machine Identity Security Access Requests. SaaS Release Notes - July 24, 2026 · Jul 2026 · source · release history
example
-
Use dynamic user input to configure machine identity accounts securely.
Generate account using `$(userInput.technicalkey)` in generator form inputsSaaS Release Notes - August 28, 2026 · Aug 2026 · source -
Enable a newly published custom user level as an access request entitlement.
Publish a custom user level in Identity Security Cloud; the system automatically generates a corresponding entitlement that can be enabled for access requests.SaaS Release Notes - May 22, 2026 · May 2026 · source
Approval workflow configuration shipped Gives administrators a single place to configure approval reminders, escalation chains, fallback approvers, and timeouts across all access item types.
Also counts toward: Web management console
release 8 total
-
Adds
Admin > System Settings > Feature Settings > Approval Settingstab for globally configuring approval reminders, escalations, and timeouts — including cron-string cadence, multi-level escalation chains, and a fallback approver set to an identity or governance group. Enhancement: Approvals Migration and Notification Reminders and Escalations, Regional Routing, and CC:/BCC: (2026-08-10) · Aug 2026 · source · release history -
Email templates now support configuring CC:/BCC: recipients from Manager, Identity, Governance Groups, Org Admins, and/or a static email address (restricted on
cloud_user_password_expiration,cloud_user_password_reset_token,cloud_user_unlock_token,cloud_user_verification_token, and… Enhancement: Approvals Migration and Notification Reminders and Escalations, Regional Routing, and CC:/BCC: (2026-08-10) · Aug 2026 · source · release history - Supports defining independent reminder and escalation configurations — reminders without escalations, escalations without reminders, and custom escalation targets outside the approver's management chain. Enhancement: Approvals Migration and Notification Reminders and Escalations, Regional Routing, and CC:/BCC: (2026-08-10) · Aug 2026 · source · release history
- Adds per-access-item reminder and escalation configuration under the Access Requests section for Entitlements, Access Profiles, and Roles, overriding the global config for those items. Enhancement: Approvals Migration and Notification Reminders and Escalations, Regional Routing, and CC:/BCC: (2026-08-10) · Aug 2026 · source · release history
- Pending approvals that have been open for longer than 90 days will begin expiring starting August 10, 2026; any remaining open pre-migration approvals will be closed. Enhancement: Approvals Migration and Notification Reminders and Escalations, Regional Routing, and CC:/BCC: (2026-08-10) · Aug 2026 · source · release history
-
Allows filtering access requests by Current Owner, Requested For, and Requested By on the
Admin > Approval Managementpage for inactive identities SaaS Release Notes - July 31, 2026 · Jul 2026 · source · release history
example
-
Add CC: recipients to an approval notification template so managers are copied on access-request decisions.
In the console, open the target email template (e.g., an access-request approval template), navigate to the CC:/BCC: configuration, select recipients from Manager, Governance Group, or enter a static…Enhancement: Approvals Migration and Notification Reminders and Escalations, Regional Routing, and CC:/BCC: (2026-08-10) · Aug 2026 · source
Data Access Security resource and permission browsing shipped Lets reviewers browse data resources in a hierarchical tree and inspect the full permission path for any user's access, including whether that access is actively used.
release
- Supports visualization of multiple permission paths to a single resource within Permissions-type campaigns. New Capability: View Permission Paths Now Available for Campaign Reviewers (2026-07-02) · Jul 2026 · source · release history
- New hierarchical tree view supports expanding and collapsing major integrations (AWS, Azure, Box, GDrive, OneDrive) and nested drive structures within the selector. Enhancement: Data Access Security Resource Selector Redesign (2026-07-02) · Jul 2026 · source · release history
- Permission Path icon is available for User permission rows and visible-but-disabled for Group permission rows, giving reviewers clear context on scope. New Capability: View Permission Paths Now Available for Campaign Reviewers (2026-07-02) · Jul 2026 · source · release history
- Adds free-text search bar (Search by name or path) to the Resource Selector, enabling instant navigation to resources without manually drilling through folder hierarchies. Enhancement: Data Access Security Resource Selector Redesign (2026-07-02) · Jul 2026 · source · release history
- Introduces a new Browse and Select Resources overlay in Data Access Security, replacing the previous compact resource picker with a full-view modal. Enhancement: Data Access Security Resource Selector Redesign (2026-07-02) · Jul 2026 · source · release history
- New View Permission Path action in the Actions column of the Campaign Review screen opens a pop-up showing the full permission path for a user's access, including whether access is actively used. New Capability: View Permission Paths Now Available for Campaign Reviewers (2026-07-02) · Jul 2026 · source · release history
docs
- # SailPoint Data Access Security Connectors ## Terminology Connector - The collection of features, components, and capabilities that comprise Data Access Security support for an integration with a managed application or endpoint. seen Oct 2026 · source
example
-
Use the new overlay to quickly locate a deeply nested cloud resource when building a Forensics permission filter.
In the console, go to Forensics > Permissions, set Attribute to 'Resource' and Operator to 'Any Of', then click the Value field — the new Browse and Select Resources overlay opens.Enhancement: Data Access Security Resource Selector Redesign (2026-07-02) · Jul 2026 · source -
Review how a user obtained access to a sensitive resource without leaving the certification screen during a Permissions-type campaign.
In the DAS console, go to My Tasks > Access Certification, select the desired Permissions-type campaign, locate the user row in the review table, and click the Permission Path icon in the Actions…New Capability: View Permission Paths Now Available for Campaign Reviewers (2026-07-02) · Jul 2026 · source
NERM Classic Workflow History shipped Adds a history tab to the NERM Classic workflow configuration view displaying version-lifecycle and step-change events.
release
- Adds a History tab to the NERM Classic workflow configuration view that displays a paginated table of version-lifecycle and step/configuration-change events. Enhancement: Workflow Versioning — History tab (2026-09-24) · Sep 2026 · source · release history
- Enables searching by step label, step ID, or version ID within the new History tab for faster navigation through workflow changes. Enhancement: Workflow Versioning — History tab (2026-09-24) · Sep 2026 · source · release history
- Adds a History tab inside the NERM Classic workflow configuration UI. Enhancement: Workflow Versioning — History tab (2026-09-23) · Sep 2026 · source · release history
- Adds a History tab to NERM Classic workflow configuration, showing a paginated newest-first table of version-lifecycle and step/configuration-change events — including when, who, event type, step label, and version identifier — without requiring Admin Activity or the audit API.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enhancement: Workflow Versioning — History tab (2026-09-23) · Sep 2026 · source · release history
- Supports search by step labels, step IDs, and version IDs within the History tab, with quick filters to narrow the event list. Enhancement: Workflow Versioning — History tab (2026-09-23) · Sep 2026 · source · release history
example
-
Audit who changed a specific workflow step and what version that change produced, without digging through Admin Activity logs.
1. Open the NERM Classic Admin console and navigate to the workflow you want to audit. 2. Select the 'History' tab. 3. In the search box, enter the step label or step ID you are investigating. 4.Enhancement: Workflow Versioning — History tab (2026-09-24) · Sep 2026 · source -
Review version history and step changes for an active NERM Classic workflow without using the audit API.
In the workflow configuration interface, select the `History` tab to view version lineage.Enhancement: Workflow Versioning — History tab (2026-09-23) · Sep 2026 · source -
Review the full change history of a NERM Classic workflow after a suspected misconfiguration, filtering by version ID to isolate the offending change.
1. Open the target workflow in NERM Classic Admin. 2. Select the 'History' tab. 3. Enter the version ID in the search box to filter events. 4.Enhancement: Workflow Versioning — History tab (2026-09-23) · Sep 2026 · source
Salesforce connector authentication shipped Migrates the Salesforce connector to OAuth 2.0 External Client App authentication, replacing all legacy auth methods by October 2026.
release 7 total
-
Extends mandatory TLS-only enforcement to the
ScriptExecutor(native before/after script execution) andgMSAPasswordData(gMSA password retrieval) privileged services — both are silently disabled if TLS is not exclusively configured on the IQService instance. New Capability: Integration Service (IQService-August-2026) is now LIVE! (2026-08-17) · Aug 2026 · source · release history - Backward compatibility toggle available in the connector UI during the 90-day migration window (July 1–September 30, 2026) to temporarily revert to legacy auth if issues arise. Announcement: Salesforce External Client App is now Available (2026-06-24) · Jun 2026 · source · release history
- Adds support for Salesforce External Client App (ECA) authentication as the new default and only supported auth method for the ISC Salesforce connector (VA and SaaS). Announcement: Salesforce External Client App is now Available (2026-06-24) · Jun 2026 · source · release history
- New Enable External Client App (ECA) toggle and ECA Authentication section available in the Identity Security Cloud UI Salesforce connector configuration. Announcement: Salesforce External Client App is now Available (2026-06-24) · Jun 2026 · source · release history
- Basic Authentication, OAuth 2.0 JWT Bearer, OAuth 2.0 Refresh Token, and OAuth 2.0 Client Credentials are permanently removed from the ISC Salesforce connector (VA and SaaS) on October 1, 2026; connectors not migrated to External Client App (ECA) Authentication will lose Salesforce connectivity and all connector… Announcement: Salesforce External Client App is now Available (2026-06-24) · Jun 2026 · source · release history
- Supports OAuth 2.0 Authorization Code Grant flow exclusively, replacing JWT Bearer, Refresh Token, Client Credentials, and Basic Authentication. Announcement: Salesforce External Client App is now Available (2026-06-24) · Jun 2026 · source · release history
example
-
Enable ECA authentication on an existing ISC Salesforce connector to maintain connectivity before the September 30, 2026 deadline.
In the Identity Security Cloud UI, open the Salesforce connector > go to the ECA Authentication section > turn on 'Enable External Client App (ECA)' > under Client Configuration, add key 'host_name'…Announcement: Salesforce External Client App is now Available (2026-06-24) · Jun 2026 · source
Data Classification scanning shipped Lets administrators configure what percentage of documents are sampled during a Data Classification scan to quickly locate sensitive-data hot spots without scanning everything.
release
- Introduces sampling rate technology in Data Access Security > Data Classification to map data assets with minimal network impact. SaaS Release Notes - June 26, 2026 · Jun 2026 · source · release history
- New Sampling Ratio option for Data Classification scans lets you scan a configurable percentage of documents (default 10% for new apps) to rapidly identify sensitive-data hot spots without a full resource-intensive scan. New Capability: Accelerated Data Discovery with Sampling Ratio (2026-06-24) · Jun 2026 · source · release history
- New applications are automatically onboarded with 10% sampling enabled by default, accelerating time-to-insight for sensitive data exposure. New Capability: Accelerated Data Discovery with Sampling Ratio (2026-06-24) · Jun 2026 · source · release history
- Existing applications with Data Classification enabled retain 100% sampling by default to preserve consistency with prior behavior. New Capability: Accelerated Data Discovery with Sampling Ratio (2026-06-24) · Jun 2026 · source · release history
- New Sampling Ratio sliding-scale control added to the Application Scope edit screen under Compliance > Data Classification > Application Scope. New Capability: Accelerated Data Discovery with Sampling Ratio (2026-06-24) · Jun 2026 · source · release history
example
-
Enable sampling in Data Access Security to quickly map sensitive data landscapes without network overhead.
Navigate to Compliance > Data Classification > Application Scope and configure the new sampling rate technology.SaaS Release Notes - June 26, 2026 · Jun 2026 · source -
Quickly surface sensitive-data hot spots in a newly integrated application before committing to a full scan.
In the console, go to Admin > Applications > Add New, complete the application setup, then on the Data Classification configuration screen set the Sampling Ratio to your desired percentage (default…New Capability: Accelerated Data Discovery with Sampling Ratio (2026-06-24) · Jun 2026 · source -
Tune the sampling percentage on an existing application to balance discovery speed against scan coverage.
In the console, go to Compliance > Data Classification > Application Scope, locate the application, click Edit, and adjust the Sampling Ratio sliding scale to the desired value.New Capability: Accelerated Data Discovery with Sampling Ratio (2026-06-24) · Jun 2026 · source
Delimited File Connector SMB/Kerberos transport shipped Adds SMB2/SMB3 as a file transport option on the VA-based Delimited File Connector, enabling direct aggregation from Windows File Server and Samba shares using Kerberos authentication, with Test Connection validation for login, share access, and file readability.
release
-
Adds
File Transport = SMBas a supported transport option to the Delimited File Connector on Identity Security Cloud Virtual Appliance Enhancement: Delimited File Connector - SMB File Transport with Kerberos Authentication (2026-10-05) · Oct 2026 · source · release history - Enables Kerberos authentication for reading identity files directly from Windows File Server or Samba shares Enhancement: Delimited File Connector - SMB File Transport with Kerberos Authentication (2026-10-05) · Oct 2026 · source · release history
- Returns explicit success or failure messages for authentication, path, permission, and network errors when using Test Connection to validate Kerberos login, share access, and file read before scheduling aggregation. Enhancement: Delimited File Connector - SMB File Transport with Kerberos Authentication (2026-10-05) · Oct 2026 · source · release history
-
Adds
SMBas a File Transport option on the VA-based Delimited File Connector, enabling direct aggregation from Windows File Server and Samba shares over SMB2/SMB3 without staging files to SFTP or S3.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enhancement: Delimited File Connector - SMB File Transport with Kerberos Authentication (2026-10-05) · Oct 2026 · source · release history -
Supports Kerberos authentication for SMB transport, configured via Host (FQDN), Port (default
445), Share Name, Kerberos Realm, Username, Password, and optional Kerberos Configuration Directory (folder on the VA containingkrb5.conf) fields in source configuration. Enhancement: Delimited File Connector - SMB File Transport with Kerberos Authentication (2026-10-05) · Oct 2026 · source · release history
example
-
Validate Kerberos login, share access, and file readability before scheduling aggregation — navigate to the source connection settings and run Test Connection.
In Identity Security Cloud, go to Admin > Connections > Sources > <your Delimited File source> > Connection Settings, set File Transport to SMB and fill in the Kerberos fields, then click 'Test…Enhancement: Delimited File Connector - SMB File Transport with Kerberos Authentication (2026-10-05) · Oct 2026 · source -
Configure a VA-based Delimited File source to pull identity files directly from a Samba AD share using Kerberos, avoiding an SFTP staging step.
File Transport: SMB Host: fileserver.lab.test Port: 445 Share Name: \\fileserver\identities Kerberos Realm: LAB.TEST Username: svc_sailpoint Password: <encrypted secret> Kerberos Configuration…Enhancement: Delimited File Connector - SMB File Transport with Kerberos Authentication (2026-10-05) · Oct 2026 · source
HashiCorp Vault non-human identity discovery connector shipped Discovers and aggregates Vault token and userpass account metadata as non-human identities in Identity Security Cloud via the Virtual Appliance, surfacing them as Dataset resources without reading secret payloads.
Also counts toward: On-premises appliance
release
- Adds a new HashiCorp Vault (On-Premise) ISC Source connector that discovers and aggregates Vault token metadata (issue/expiration time, policies, token type) and userpass account metadata (username, policies, token TTL/period settings) as non-human identities — without reading secret payloads.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New Capability: HashiCorp Vault (On-Premise) Connector for NHI Discovery (2026-10-05) · Oct 2026 · source · release history
- Surfaces NHI metadata as Dataset resources in Identity Security Cloud: Vault tokens modeled as credentials, and Vault userpass accounts modeled as machine accounts. New Capability: HashiCorp Vault (On-Premise) Connector for NHI Discovery (2026-10-05) · Oct 2026 · source · release history
- Provides Test Connection validation capability for the new Virtual Appliance-based connection to on-prem Vault. New Capability: HashiCorp Vault (On-Premise) Connector for NHI Discovery (2026-10-05) · Oct 2026 · source · release history
- Connects to on-premises HashiCorp Vault Community edition through the Virtual Appliance using the Vault host URL and an API token, keeping the existing HashiCorp Vault Credential Provider unchanged. New Capability: HashiCorp Vault (On-Premise) Connector for NHI Discovery (2026-10-05) · Oct 2026 · source · release history
- Supports both Express and standard source setup, with a Test Connection step to validate connectivity before aggregation. New Capability: HashiCorp Vault (On-Premise) Connector for NHI Discovery (2026-10-05) · Oct 2026 · source · release history
- Adds a new HashiCorp Vault (On-Premise) source connector to discover and aggregate non-human identity metadata from on-premises Vault Community edition. New Capability: HashiCorp Vault (On-Premise) Connector for NHI Discovery (2026-10-05) · Oct 2026 · source · release history
example
-
Onboard an on-prem HashiCorp Vault Community instance to start inventorying Vault token and userpass non-human identities in Identity Security Cloud.
In ISC Admin, go to Connections > Sources > Add Source, select 'HashiCorp Vault (On-Premise)', enter the Vault host URL and API token, choose your Virtual Appliance, click 'Test Connection', then run…New Capability: HashiCorp Vault (On-Premise) Connector for NHI Discovery (2026-10-05) · Oct 2026 · source
Java EE to Jakarta EE 10 Modernization shipped Moves IdentityIQ to the Jakarta EE 10 stack with an upgrade pre-check utility and updated application server support.
release 7 total
- Delivers a single forward IdentityIQ release line, consolidating all future capabilities — including Metadata Campaigns, time-based access controls, and modernized application definitions — onto the Jakarta EE 10 stack. IdentityIQ 9.0 and Jakarta EE: a modern application-server foundation for self-hosted IGA (2026-09-24) · Sep 2026 · source · release history
- Supports Jakarta EE 10 as the new application-server foundation, enabling IdentityIQ to run on current LTS runtimes: Apache Tomcat 10.1.40, Tomcat 11.0.6, JBoss EAP, and WebSphere Liberty.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ IdentityIQ 9.0 and Jakarta EE: a modern application-server foundation for self-hosted IGA (2026-09-24) · Sep 2026 · source · release history
- Introduces the IdentityIQ 9.0 Upgrade Pre-Check Utility, which inventories Java EE customizations and generates proposed Jakarta EE updates for team review and testing. IdentityIQ 9.0 and Jakarta EE: a modern application-server foundation for self-hosted IGA (2026-09-24) · Sep 2026 · source · release history
-
Inventories Connector Registry application templates that still use
.xhtmlform or access files instead of the new XML source configuration format Announcing the IdentityIQ 9.0 Upgrade Pre-Check Utility (2026-08-26) · Aug 2026 · source · release history - Enables automated output of transformed Jakarta-safe file copies to a separate directory while preserving originals for review Announcing the IdentityIQ 9.0 Upgrade Pre-Check Utility (2026-08-26) · Aug 2026 · source · release history
-
Provides
Precheck-userguide.pdfandSourceConfigXMLReferenceGuide.pdfalongside the utility for installation and XML format details Announcing the IdentityIQ 9.0 Upgrade Pre-Check Utility (2026-08-26) · Aug 2026 · source · release history
Databricks connector for Data Access Security shipped Discovers Databricks resources and permissions, ingests native classification labels, and flags over-permissioned accounts for remediation.
release
- Enables permission collection for users, groups, and service accounts in enterprise identity terms New Capability: Data Access Security - Google BigQuery Connector (2026-10-05) · Oct 2026 · source · release history
- The Databricks connector for Data Access Security is available to customers, supporting structured data crawling, object-level permission analysis, and ingestion of Data Classification labels. SaaS Release Notes - July 10, 2026 · Jul 2026 · source · release history
- New Databricks connector for Data Access Security (DAS) enables discovery of Databricks resources including Tables, Views, and Stored Procedures. New Capability: Data Access Security (DAS) for DataBricks (2026-07-09) · Jul 2026 · source · release history
- Ingests data classification labels directly from Databricks (when enabled), surfacing classification forensics within the DAS platform (preview). New Capability: Data Access Security (DAS) for DataBricks (2026-07-09) · Jul 2026 · source · release history
- Supports permission analysis to detect over-permissioned accounts and limit entitlement sprawl across Databricks deployments. New Capability: Data Access Security (DAS) for DataBricks (2026-07-09) · Jul 2026 · source · release history
- Unifies Databricks governance with existing SailPoint frameworks covering applications, infrastructure, and file storage systems. New Capability: Data Access Security (DAS) for DataBricks (2026-07-09) · Jul 2026 · source · release history
Data Access Security Classification Ingestion shipped Enables Data Access Security applications to import data classification results from third-party DSPM vendors or upload CSVs.
Also counts toward: Import from a competing product
release
-
Enables each Data Access Security application to run either the native classification engine or import results from a third-party DSPM vendor (Purview, Cyera, BigID).
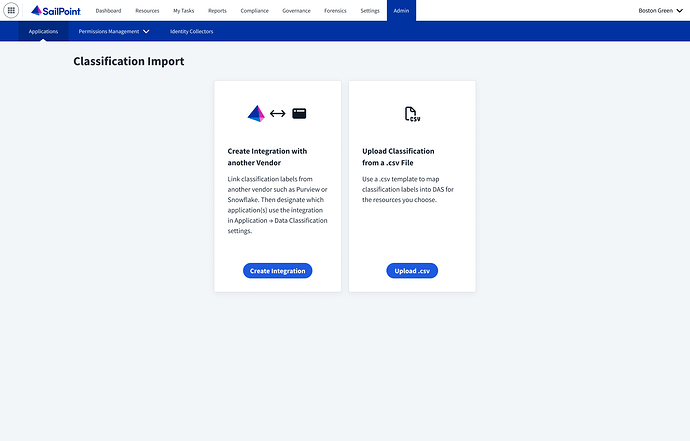 New Capability: Purview, Cyera & BigID Data Classification Labels Integration in Data Access Security (2026-09-24) · Sep 2026
· source
· release history
- Supports scheduled imports so classification labels stay current without manual re-runs, configurable per application in Data Access Security. New Capability: Purview, Cyera & BigID Data Classification Labels Integration in Data Access Security (2026-09-24) · Sep 2026 · source · release history
- Exposes classification import configuration under Compliance → Data Classification → Classification Import in the SailPoint ISC console. New Capability: Purview, Cyera & BigID Data Classification Labels Integration in Data Access Security (2026-09-24) · Sep 2026 · source · release history
- Adds a Classification Label Import wizard in Data Access Security to onboard Microsoft Purview, Cyera, or BigID as data classification sources, or upload a CSV, eliminating duplicate classification runs.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New Capability: Purview, Cyera & BigID Data Classification Labels Integration in Data Access Security (2026-09-24) · Sep 2026 · source · release history
- Adds automatic revocation configuration for SharePoint Online and OneDrive records in Data Access Security campaigns SaaS Release Notes - May 15, 2026 · May 2026 · source · release history
example
-
Bring Purview classification labels into ISC entitlements so your access reviews reflect actual data sensitivity — without re-running classification.
In the SailPoint ISC console: 1. Go to Data Access Security and onboard your data source application. 2. Select 'Import data classification' during application setup. 3.New Capability: Purview, Cyera & BigID Data Classification Labels Integration in Data Access Security (2026-09-24) · Sep 2026 · source
New Certification Engine shipped Introduces a new certification engine that scales campaign generation to multi-million items and reduces large campaign generation time from days to minutes.
release
- Introduces a new certification engine that scales campaign generation to multi-million items, reducing large campaign generation time from days to minutes.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GA Announcement: Next Generation Certifications (2026-09-22) · Sep 2026 · source · release history
- Adds a Generate and Start option so small campaigns kick off immediately after generation without requiring a manual start step. GA Announcement: Next Generation Certifications (2026-09-22) · Sep 2026 · source · release history
- Adds Generate and Start availability for campaigns launched from workflows, replacing the legacy manual-start pattern for targeted certifications. GA Announcement: Next Generation Certifications (2026-09-22) · Sep 2026 · source · release history
- Administrators can access campaigns generated before cutover under Legacy Campaigns in the left navigation. GA Announcement: Next Generation Certifications (2026-09-22) · Sep 2026 · source · release history
- Adds Generate and Start option for campaigns to bypass manual composition review steps. GA Announcement: Next Generation Certifications (2026-09-22) · Sep 2026 · source · release history
example
-
After cutover, locate pre-migration campaigns that are no longer on the active list by navigating to the Legacy Campaigns view in the admin console.
In the SailPoint admin console, go to Certifications > Legacy Campaigns in the left navigation to view and manage campaigns generated before your tenant cutover date.GA Announcement: Next Generation Certifications (2026-09-22) · Sep 2026 · source
Data Access Security (DAS) dashboard shipped Provides a pre-built dashboard template that gives instant visibility into unstructured data access exposure and high-risk accounts, with drill-down into forensics.
release
- Updates UI so application navigation bar is always visible on Admin pages including Sources, Discovery Connectors, Virtual Appliances, Credential Providers, Identities, Accounts, Roles, Access Profiles, Entitlements, Campaigns, Email Templates, and Forms. SaaS Release Notes - August 21, 2026 · Aug 2026 · source · release history
- Adds a suite of Data Access Security (DAS) widgets to the MySailPoint homepage, enabling instant visibility into unstructured data access exposure and high-risk accounts with excessive permissions. New Capability: Customizable DAS Insights on ISC Homepage (2026-06-29) · Jun 2026 · source · release history
- Enables drill-down from any DAS widget directly into Data Access Security forensics for deeper analysis of flagged metrics. New Capability: Customizable DAS Insights on ISC Homepage (2026-06-29) · Jun 2026 · source · release history
- Introduces a pre-built Data Access Security Dashboard template that bundles all available DAS widgets for quick, one-click setup. New Capability: Customizable DAS Insights on ISC Homepage (2026-06-29) · Jun 2026 · source · release history
docs
- # Data Access Security SailPoint Data Access Security empowers organizations to discover, govern, and secure sensitive data and protect it from critical security risks. seen Oct 2026 · source
example
-
Quickly stand up a unified DAS monitoring view for your security team without manually assembling individual widgets.
In the ISC console, go to MySailPoint Homepage > Dashboards > Dashboard Templates and select 'Data Access Security Dashboard' to instantiate the pre-built template.New Capability: Customizable DAS Insights on ISC Homepage (2026-06-29) · Jun 2026 · source
Custom metadata attributes for access objects shipped Lets administrators attach and search by custom metadata on roles, access profiles, and entitlements to enrich governance data.
release
- Extends access model metadata custom attributes to allow ad hoc values up to 100 characters, with limits expanded to 250 attributes per access object type and 5,000 values per attribute SaaS Release Notes - July 31, 2026 · Jul 2026 · source · release history
- Adds Allow Multivalued Assignment option on custom metadata attributes, permitting more than one value to be assigned to a single attribute (note: once enabled, cannot be undone). New Capability: Access Model Metadata Adhoc Values (2026-07-27) · Jul 2026 · source · release history
- Expands value capacity to up to 5,000 different values per custom attribute and up to 250 custom metadata attributes per access object type. New Capability: Access Model Metadata Adhoc Values (2026-07-27) · Jul 2026 · source · release history
- Ad hoc values entered while Allow Ad Hoc Values is enabled are retained even if the option is later disabled. New Capability: Access Model Metadata Adhoc Values (2026-07-27) · Jul 2026 · source · release history
- Enables search for roles, access profiles, and entitlements by ad hoc metadata attribute values. New Capability: Access Model Metadata Adhoc Values (2026-07-27) · Jul 2026 · source · release history
- Adds Allow Ad Hoc Values option when creating or editing a custom metadata attribute, enabling free-form values up to 100 characters per value — no pre-defined list required — on roles, access profiles, and entitlements. New Capability: Access Model Metadata Adhoc Values (2026-07-27) · Jul 2026 · source · release history
SAP Concur Connector Spend API V4.1 Migration shipped Upgrades the connector to retrieve spend data via the V4.1 API, shifting response fields to strict camel-case technical names while preserving legacy label mapping for backward compatibility.
release
-
Adds
useSpendApiV41application XML entry to the SAP Concur connector config, enabling administrators to opt existing sources into Spend API V4.1 on their own schedule.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New Capability: SAP Concur Connector Updated to Support Spend API V4.1 (2026-10-12) · Oct 2026 · source · release history -
Existing
jsonPathMappingentries that referencecustomDatalabels will break under Spend API V4.1: V4.1 returns strict camel-case technical field names instead of the human-readable labels returned by V4. New Capability: SAP Concur Connector Updated to Support Spend API V4.1 (2026-10-12) · Oct 2026 · source · release history - Updates the SAP Concur SaaS & VA connector to use Spend API V4.1 for Spend User retrieval, replacing the deprecated Spend API V4; sources created on or after June 1, 2026 use V4.1 by default. New Capability: SAP Concur Connector Updated to Support Spend API V4.1 (2026-10-12) · Oct 2026 · source · release history
-
Changes
customDataresponse format from label-based field names (V4) to strict camel-case technical field names (V4.1), requiring review and update of existingjsonPathMappingentries that referencecustomData. New Capability: SAP Concur Connector Updated to Support Spend API V4.1 (2026-10-12) · Oct 2026 · source · release history
example
-
Opt an existing SAP Concur source (created before June 1, 2026) into Spend API V4.1 after reviewing and updating customData mappings.
<entry key="useSpendApiV41" value="true"/> <!-- Updated customData mapping pattern --> <entry key="orgUnit1"…New Capability: SAP Concur Connector Updated to Support Spend API V4.1 (2026-10-12) · Oct 2026 · source
Confluence Cloud connector for Data Access Security shipped Adds a Confluence Cloud connector to Data Access Security that inventories spaces, pages, and attachments with effective-permission mapping in enterprise identity terms, surfaces unresolved-principal markers for unmatched identities, and supports data classification of unstructured Confluence content using the existing DAS classification approach.
release
- Adds Atlassian Confluence Cloud connector to Data Access Security for inventory, effective permissions analysis, and unstructured content classification. New Capability: Data Access Security - Atlassian Confluence Connector (2026-10-05) · Oct 2026 · source · release history
- Adds a Confluence Cloud connector to Data Access Security, enabling inventory of Confluence spaces, pages, and attachments with effective-permission mapping expressed in enterprise identity terms.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New Capability: Data Access Security - Atlassian Confluence Connector (2026-10-05) · Oct 2026 · source · release history
- Surfaces unresolved-principal markers when a Confluence principal cannot be matched to a known identity, making permission gaps explicit. New Capability: Data Access Security - Atlassian Confluence Connector (2026-10-05) · Oct 2026 · source · release history
- Supports data classification of unstructured Confluence content using the existing DAS classification approach, extending the same governance model already applied to other data sources. New Capability: Data Access Security - Atlassian Confluence Connector (2026-10-05) · Oct 2026 · source · release history
example
-
Onboard a Confluence Cloud site into Data Access Security to begin crawling spaces, pages, and attachments and collecting effective permissions.
In the DAS console, go to Applications > Add Application, select 'Confluence Cloud', enter your Confluence site URL and credentials with the documented Confluence permissions, then run Crawl,…New Capability: Data Access Security - Atlassian Confluence Connector (2026-10-05) · Oct 2026 · source
Quick Compliance and Read-Only Sources shipped Adds Quick Compliance support for multiple new sources and expands read-only source coverage to include additional tools like Anvil, DataHub, and Redpanda.
release
- Expands Quick Compliance support to include Anvil, DataHub, Employment Hero, Fibery, Freshcaller, Juniper Mist, LangChain, noCRM, Redpanda Cloud Control Plane, and UserVoice as read-only sources for account/entitlement aggregation. SaaS Release Notes - September 25, 2026 · Sep 2026 · source · release history
- Adds Quick Compliance support for 13 new sources: Checkmk, Cloudiway, Condens, FOSSA, Infisical, Kashoo, Nifty, Qdrant, Scrive, StackHawk, Trigger, Vendasta, and YouSign SaaS Release Notes - September 18, 2026 · Sep 2026 · source · release history
- Adds Exotel, Grist, SafetyCulture, Tenable-io, and Zylo as Quick Compliance connectors for expedient read-only account and entitlement aggregation SaaS Release Notes - July 3, 2026 · Jul 2026 · source · release history
docs
- Anvil Checkmk Cloudiway Condens DataHub Employment Hero FOSSA Freshcaller Infisical Juniper Mist Kashoo LangChain Nifty noCRM Qdrant Redpanda Cloud Control Plane Scrive StackHawk Trigger Vendasta YouSign docs update · Sep 2026 · source
example
-
Configure a new Quick Compliance source (e.g., Logrhythm) for rapid read-only account aggregation via the platform UI.
Go to SaaS Connectors, select 'Quick Compliance' sources, and configure the Logrhythm connector settings.SaaS Release Notes - June 26, 2026 · Jun 2026 · source
Separation of Duty Policy Criteria shipped Enables configuring Access Profiles and SailPoint Roles within Separation of Duty policy lists for mixed access control rules.
release
- Expands SoD policy criteria in Identity Security Cloud to include roles and access profiles alongside entitlements SaaS Release Notes - September 11, 2026 · Sep 2026 · source · release history
- Allows Separation of duties permissions to be included in custom user levels SaaS Release Notes - September 4, 2026 · Sep 2026 · source · release history
- Enables SoD Violation Management and SoD Violation Controls for FedRAMP customers licensed for Separation of Duties SaaS Release Notes - September 4, 2026 · Sep 2026 · source · release history
-
Adds support for Access Profiles in SoD policy criteria, enabling mixed criteria across lists (e.g., entitlements in List A and a Role in List B).
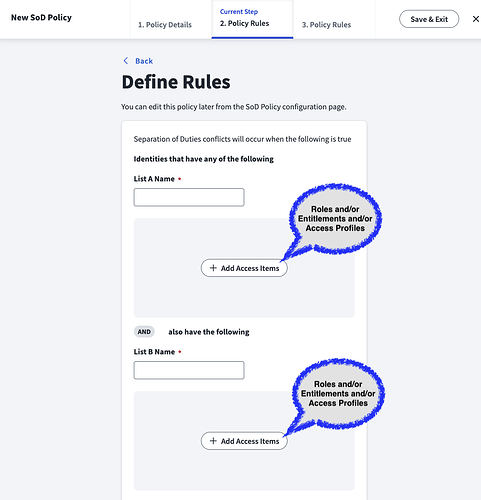 New Capability: Roles Criteria in SoD Policy Definition (2026-08-03) · Aug 2026
· source
· release history
- Adds support for SailPoint Roles in Separation of Duty (SoD) policy List A and List B criteria, configurable via Admin → Policies → Separation of Duty. New Capability: Roles Criteria in SoD Policy Definition (2026-08-03) · Aug 2026 · source · release history
Email sender regionalization shipped Sends email from the tenant's own AWS region rather than always routing through a single US region, and records the sending region on audit events.
Also counts toward: Administrative audit log
release
-
New identities (email addresses and domains) are now created and verified in the tenant's primary AWS region rather than always routing through
us-east-1. Enhancement: Approvals Migration and Notification Reminders and Escalations, Regional Routing, and CC:/BCC: (2026-08-10) · Aug 2026 · source · release history -
Adds a
regionfield toEMAIL_SENTaudit events, reflecting the AWS region used to send each email. Enhancement: Approvals Migration and Notification Reminders and Escalations, Regional Routing, and CC:/BCC: (2026-08-10) · Aug 2026 · source · release history -
Existing verified sender email addresses are not auto-migrated and continue to send from
us-east-1; they must be manually removed and re-added to trigger verification in the primary region. Enhancement: Approvals Migration and Notification Reminders and Escalations, Regional Routing, and CC:/BCC: (2026-08-10) · Aug 2026 · source · release history -
Domains with a custom
MAIL FROMattribute configured will NOT be automatically migrated to the primary region — owners must manually re-add and re-verify the domain in their primary region or emails risk being blocked by SMTP servers. Enhancement: Approvals Migration and Notification Reminders and Escalations, Regional Routing, and CC:/BCC: (2026-08-10) · Aug 2026 · source · release history
example
-
Migrate a verified sender domain to your primary AWS region so emails no longer route through us-east-1.
In the console, go to the email identities section, locate the domain showing the 'us-east-1' region label, remove it, and re-add the same domain — the new entry will replace the existing record and…Enhancement: Approvals Migration and Notification Reminders and Escalations, Regional Routing, and CC:/BCC: (2026-08-10) · Aug 2026 · source
AI-driven privilege classification recommendations shipped Surfaces AI-generated suggestions for entitlements that may be privileged, and lets owners accept, reject, or delegate the classification decision with a full audit trail.
Also counts toward: Administrative audit log
release
- Enables delegation of recommendations to entitlement owners, source owners, governance groups, or other subject matter experts using the existing approvals flow. New Capability: Auto-Discovery of Privileged Entitlements (2026-08-03) · Aug 2026 · source · release history
- Surfaces recommendations for potentially privileged entitlements based on aggregate privilege classification pattern analysis, covering access that falls outside vendor-published lists or custom criteria. New Capability: Auto-Discovery of Privileged Entitlements (2026-08-03) · Aug 2026 · source · release history
- Maintains an auditable record of all privilege classification decisions for governance and compliance tracking. New Capability: Auto-Discovery of Privileged Entitlements (2026-08-03) · Aug 2026 · source · release history
- Integrates recommendations into existing entitlement and source pages, allowing administrators to accept or reject each recommendation and assign a privilege level when marking an entitlement as privileged. New Capability: Auto-Discovery of Privileged Entitlements (2026-08-03) · Aug 2026 · source · release history
- Identity Security Cloud introduces AI Privilege Discovery to identify high-risk entitlements and automatically present privilege level recommendations for review. SaaS Release Notes - July 10, 2026 · Jul 2026 · source · release history
Virtual Appliance network infrastructure shipped Routes Virtual Appliance container updates and message queue traffic through SailPoint-hosted endpoints to simplify network rules and reduce direct AWS service dependencies.
release
- Separation of Duties (SoD) now features a new UI for policy creation and violation viewing, allowing suites customers to apply controls with expiration duration to violations. SaaS Release Notes - July 10, 2026 · Jul 2026 · source · release history
-
Introduces SailPoint-hosted endpoints for VA container image updates, replacing direct Amazon ECR paths — new hostnames:
va-docker.secure-api.infra.identitynow.com(Commercial) andva-docker.secure-api.saas.sailpointfedramp.com(FedRAMP). Deprecation: Virtual Appliance network access - AWS URLs (2026-06-16) · Jun 2026 · source · release history -
Introduces SailPoint-hosted endpoints for Virtual Appliance message queue traffic, replacing direct regional Amazon SQS URLs (
sqs.<region>.amazonaws.com). Deprecation: Virtual Appliance network access - AWS URLs (2026-06-16) · Jun 2026 · source · release history - Sandbox rollout of SailPoint-hosted URLs begins June 15; production rollout begins June 29, 2026. Deprecation: Virtual Appliance network access - AWS URLs (2026-06-16) · Jun 2026 · source · release history
example
-
Add the new SailPoint-hosted Docker/ECR endpoint to your firewall allowlist before the June 29 production rollout to ensure uninterrupted VA image updates.
# Commercial environments — add to your outbound firewall allowlist: va-docker.secure-api.infra.identitynow.com # FedRAMP environments — add to your outbound firewall allowlist:…Deprecation: Virtual Appliance network access - AWS URLs (2026-06-16) · Jun 2026 · source
Mobile certification review shipped Optimises the access certification review experience on tablets so reviewers can make decisions comfortably on mobile devices.
release
- In-flight certifications pick up the improved reviewer UI automatically after tenant cutover, with no reviewer action required. GA Announcement: Next Generation Certifications (2026-09-22) · Sep 2026 · source · release history
- Delivers an optimized Certification Reviewer UX in landscape mode, presenting a comprehensive view of access items to support informed decision-making on mobile devices. Enhancement: Tablet Support for Certifications (2026-06-26) · Jun 2026 · source · release history
- Adds automatic tablet detection for Certification Reviewers, evaluating screen capabilities to determine if the reviewer UX can be displayed optimally. Enhancement: Tablet Support for Certifications (2026-06-26) · Jun 2026 · source · release history
- Introduces landscape orientation prompting on tablets, guiding reviewers to rotate their devices for full visibility of access review tables and critical details. Enhancement: Tablet Support for Certifications (2026-06-26) · Jun 2026 · source · release history
Outbound Email Authentication shipped Configures OAuth-based SMTP authentication for outbound communications to ensure compatibility with modern Exchange environments.
release
- Adds Kerberos authentication support for Microsoft Exchange Server integrations. File Access Manager 8.5 Service Pack 2 Released! (2026-09-09) · Sep 2026 · source · release history
- Adds OAuth-based SMTP authentication for outbound email communications, replacing Basic Authentication for Exchange Online compatibility. File Access Manager 8.5 Service Pack 2 Released! (2026-09-09) · Sep 2026 · source · release history
- Adds Kerberos authentication support for Microsoft Exchange Server environments File Access Manager 8.5 Service Pack 2 Released! (2026-09-09) · Sep 2026 · source · release history
- Adds SMTP OAuth authentication support for outbound emails File Access Manager 8.5 Service Pack 2 Released! (2026-09-09) · Sep 2026 · source · release history
AI assistant access request management shipped Lets users search the access catalog, submit requests, check approval status, and cancel requests through a conversational AI assistant.
Also counts toward: Built-in AI assistant, Natural-language query
release
-
Adds the Harbor Pilot Access Request Agent for entitled customers, enabling natural-language access request search, interactive selection, form submission, request cancellation with a reason, and request status reporting.
New Capability: Next-Gen Access Request (2026-09-08) · Sep 2026
· source
· release history
- Adds cross-field catalog search in Find Access, searching across name, description, source, application, owner, privilege, and access model metadata — with filters for roles, access profiles, entitlements, and applications. New Capability: Next-Gen Access Request (2026-09-08) · Sep 2026 · source · release history
- Adds identity search by name, email, or manager when requesting for others, with a toggle between All and My Team and support for filtering on up to five public identity attributes configured by an administrator. New Capability: Next-Gen Access Request (2026-09-08) · Sep 2026 · source · release history
- AI assistants can now manage ISC access requests conversationally — search the access catalog, submit requests, check approval status, and cancel requests. Enhancement: SailPoint MCP Server Now Supports Global URL and OAuth — Connect Any AI Client in Minutes (2026-07-09) · Jul 2026 · source · release history
Mainframe (z/OS) connector modernisation shipped Modernises RACF, ACF2, and Top Secret mainframe connectors with direct agent connectivity, removing the need for a separate Connector Gateway.
release
- Adds z/OS 3.2 support to the ACF2-Full connector SaaS Release Notes - August 7, 2026 · Aug 2026 · source · release history
- Adds new security and maintainability improvements to the RACF, ACF2, and Top Secret integrations on z/OS. Closed Preview: Next-Generation Mainframe Connectors for RACF, ACF2, and Top Secret (2026-07-16) · Jul 2026 · source · release history
- Introduces direct connectivity from SailPoint Identity Management products to the SailPoint agent on the mainframe, removing the requirement to deploy and maintain a Connector Gateway. Closed Preview: Next-Generation Mainframe Connectors for RACF, ACF2, and Top Secret (2026-07-16) · Jul 2026 · source · release history
- Includes migration tooling to help transition existing configurations and customizations from the legacy connector to the new architecture. Closed Preview: Next-Generation Mainframe Connectors for RACF, ACF2, and Top Secret (2026-07-16) · Jul 2026 · source · release history
Oracle OAG Identity Lifecycle & Aggregation shipped Aggregates OAG identities and entitlements while supporting full lifecycle operations and forwarding access requests through the identity request center.
Also counts toward: Role-based access control
release
- Supports lifecycle operations — activating, terminating, enabling, disabling, and deleting OAG identities and their downstream Oracle accounts — with per-application lifecycle controls to target a specific Oracle application without affecting others. New Capability: SailPoint Oracle Access Governance SaaS Connector (2026-10-12) · Oct 2026 · source · release history
- Aggregates OAG identities as accounts and OAG roles and access bundles as entitlements, including application-level and included-permission context. New Capability: SailPoint Oracle Access Governance SaaS Connector (2026-10-12) · Oct 2026 · source · release history
- Supports access requests, grants, and revocations through the SailPoint Identity Security request center, with the connector forwarding approved requests to OAG for fulfillment — including clear provisioning results when an OAG guardrail or segregation-of-duties check prevents a request. New Capability: SailPoint Oracle Access Governance SaaS Connector (2026-10-12) · Oct 2026 · source · release history
Collaboration Portal SSO Identity Resolution shipped Configures assertion-attribute matching for SSO flows to resolve identity mapping failures when IdPs transform or hash NameIDs.
Also counts toward: REST API
release
-
Supports assertion-attribute matching (for example, email) for both pre-provisioned (non-JIT) and JIT user flows, configurable through the admin UI and API.
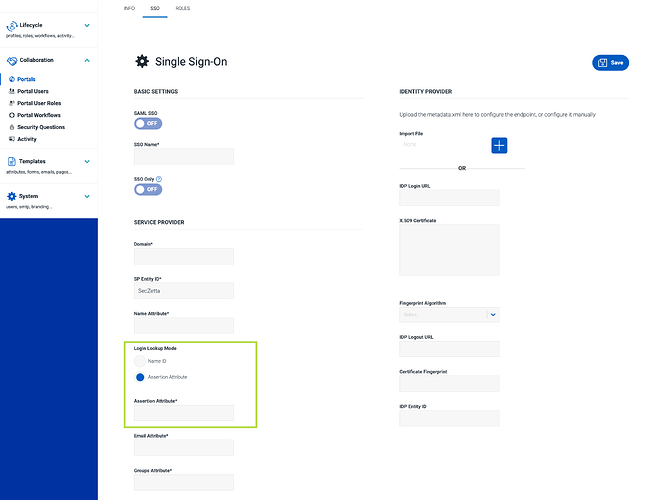 Enhancement: Collaboration Portal SSO - Flexible Identity Provider Matching (2026-10-09) · Oct 2026
· source
· release history
-
Adds Login Lookup Mode setting on the collaboration portal SSO tab, letting administrators choose between
NameID(default) and Assertion attribute matching to resolve SSO identity mapping failures when an IdP transforms or hashes the user identifier.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enhancement: Collaboration Portal SSO - Flexible Identity Provider Matching (2026-10-09) · Oct 2026 · source · release history
example
-
When your IdP transforms or hashes the NameID, switch the collaboration portal SSO matching mode to assertion attribute so pre-provisioned collaborators can authenticate.
In the admin UI, go to the collaboration portal SSO tab, locate the 'Login Lookup Mode' setting, and select 'Assertion attribute'.Enhancement: Collaboration Portal SSO - Flexible Identity Provider Matching (2026-10-09) · Oct 2026 · source
Disconnected Application Governance shipped Introduces a dedicated source type to aggregate accounts and entitlements from API-less systems and surfaces them across existing search, certification, and reporting workflows.
release
- Surfaces accounts and entitlements from disconnected applications in SailPoint's existing search, certifications, reporting, and reconciliation workflows alongside connected sources. Enhancement: Disconnected applications connector - limited availability (2026-10-09) · Oct 2026 · source · release history
- Introduces the disconnected applications connector as a new source type in Identity Security Cloud, bringing legacy web apps, custom internal tools, and API-less systems under centralized SailPoint governance. Enhancement: Disconnected applications connector - limited availability (2026-10-09) · Oct 2026 · source · release history
- Adds delta aggregation support (API and HCM Extract modes) to the Oracle HCM Cloud connector SaaS Release Notes - August 7, 2026 · Aug 2026 · source · release history
Event-Driven Integration Triggers shipped Replaces timer-based polling with mandatory event trigger subscriptions and provides scheduled reconciliation jobs to capture missed state changes during connectivity failures.
Also counts toward: REST API, Scheduled jobs
release
-
Configuring ISC event triggers is mandatory from v5.4 — existing timer-based polling is replaced and will not function; customers must create a ServiceNow integration user (roles
rest_service,x_sap_initidn.user,itil; identity type Machine, web services access only), subscribe to the five required event… Enhancement: ServiceNow Service Catalog v5.4 — Event-driven Approvals and Access Request Status Sync (2026-10-09) · Oct 2026 · source · release history -
Adds five ISC event trigger subscriptions via
https://{instance_name}.service-now.com/api/x_sap_intidn/isc_event_processorto push real-time state changes from Identity Security Cloud to ServiceNow, replacing timer-based polling.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enhancement: ServiceNow Service Catalog v5.4 — Event-driven Approvals and Access Request Status Sync (2026-10-09) · Oct 2026 · source · release history - Adds an ISC Backup Utility scheduled job to reconcile missed events during connectivity or event-delivery failures. Enhancement: ServiceNow Service Catalog v5.4 — Event-driven Approvals and Access Request Status Sync (2026-10-09) · Oct 2026 · source · release history
Google BigQuery connector for Data Access Security shipped Adds a BigQuery connector to Data Access Security that crawls and inventories BigQuery datasets, tables, views, and routines, and collects effective permissions across users, groups, and service accounts expressed in enterprise identity terms.
release
-
Adds
Google BigQueryconnector to Data Access Security (DAS) for crawling datasets, tables, views, and routines New Capability: Data Access Security - Google BigQuery Connector (2026-10-05) · Oct 2026 · source · release history - Adds a Google BigQuery connector to Data Access Security, enabling crawl and inventory of BigQuery datasets, tables, views, and routines.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New Capability: Data Access Security - Google BigQuery Connector (2026-10-05) · Oct 2026 · source · release history
- Collects effective permissions for BigQuery resources, explaining access in enterprise identity terms across users, groups, and service accounts. New Capability: Data Access Security - Google BigQuery Connector (2026-10-05) · Oct 2026 · source · release history
Governance Group Task Notifications shipped Extends task notifications to reach all members of an assigned Governance Group.
release
- Updates audit events to name the individual group member who completes a task New Capability: Manual Task Support for Governance Groups (2026-09-25) · Sep 2026 · source · release history
- Displays group-assigned manual tasks as a single row listing all assigned members in the admin task view. New Capability: Manual Task Support for Governance Groups (2026-09-25) · Sep 2026 · source · release history
- Extends existing task notifications — Pending Manual Changes, Pending Task Daily Digest, and Task Reassignment — to reach all members of an assigned Governance Group. New Capability: Manual Task Support for Governance Groups (2026-09-25) · Sep 2026 · source · release history
IdentityIQ Log Management shipped Adds a log download section in the SaaS connector UI for administrators to access connector-scoped log snapshots.
Also counts toward: Web management console
release
- Adds a log download section in the SaaS connector UI at Admin → Sources → Source Details → Advanced → Logging, letting administrators download connector-scoped log snapshots covering ~24 hours of history.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New Capability: SaaS Connector Log Download (2026-09-24) · Sep 2026 · source · release history
- Debug log level changes are reflected in downloaded snapshots, so admins can enable debug mode and re-download to capture more detail during an incident. New Capability: SaaS Connector Log Download (2026-09-24) · Sep 2026 · source · release history
example
-
Troubleshoot a SaaS connector connectivity failure without opening a support case or using the CLI.
1. In the ISC admin console, go to Admin → Sources → <your SaaS source> → Source Details → Advanced → Logging. 2. Enable 'Debug' log level. 3. Reproduce or wait for the connectivity failure. 4.New Capability: SaaS Connector Log Download (2026-09-24) · Sep 2026 · source
Workflow Audit Event Querying shipped Allows filtering and retrieval of workflow audit logs by specific workflow subject and definition identifiers.
release
- Supports filtering of new workflow audit events by workflow subject and definition identifiers using the existing Audit Events query API. New Capability: Workflow Audit and Visibility for Non-Employee Risk Management Workflows (2026-08-17) · Aug 2026 · source · release history
example
-
Review the complete history of changes for a specific NERM Classic workflow to audit who modified configurations and when.
Open an existing workflow and select History.Enhancement: Workflow Versioning — History tab (2026-09-24) · Sep 2026 · source -
Find all configuration changes for a specific step by filtering the history table.
Search by step label, step ID, or version ID in the History tab.Enhancement: Workflow Versioning — History tab (2026-09-24) · Sep 2026 · source
Next-Gen Access Request Migration shipped Migrates production tenants to the Next-Gen Access Request experience permanently, including identity search filters for requesting on behalf of others.
release
-
Opting a production tenant into Next-Gen Access Request is permanent — it cannot be rolled back to the legacy Request Center experience. All production tenants are forcibly migrated on February 16, 2027 if not opted in earlier.
New Capability: Next-Gen Access Request (2026-09-08) · Sep 2026
· source
· release history
- Adds identity search by name, email, or manager when requesting for others, with a toggle between All and My Team and support for filtering on up to five public identity attributes configured by an administrator. New Capability: Next-Gen Access Request (2026-09-08) · Sep 2026 · source · release history
- Opting into Next-Gen Access Request in production is permanent and cannot be rolled back to the legacy experience; all remaining production tenants move automatically on February 16, 2027 if not opted in by February 15, 2027 New Capability: Next-Gen Access Request (2026-09-08) · Sep 2026 · source · release history
Microsoft Entra ID Connector shipped Aggregates Microsoft Entra ID accounts, entitlements, and PIM group memberships while supporting direct assignment filtering.
release
-
Adds PIM Groups (
azureADEligibleGroupandazureADActiveGroup) support to the Microsoft Entra ID connector for aggregation and entitlement management SaaS Release Notes - July 3, 2026 · Jul 2026 · source · release history -
Enables excluding inherited
appRoleAssignmentsduring Microsoft Entra ID account aggregation to aggregate only direct assignments. SaaS Release Notes - June 26, 2026 · Jun 2026 · source · release history - Microsoft Entra SaaS connector can now be configured for Activity Insights SaaS Release Notes - May 29, 2026 · May 2026 · source · release history
HTTP/2 support shipped Enables HTTP/2 across all ISC environments for improved performance, with a note that response header keys will be lowercased and API clients may need updating.
release
-
HTTP/2 enablement in Cloudflare will cause response header keys to become lowercase (e.g., X-Total-Count becomes
x-total-count), which may break API calls or scripts that expect case-sensitive header keys in responses from ISC Maintenance: HTTP/2 Enablement in Cloudflare (2026-06-30) · Jun 2026 · source · release history -
Breaking change: HTTP/2 lowercases all response header keys (e.g., X-Total-Count becomes
x-total-count) — scripts and API clients that match headers case-sensitively must be updated. Maintenance: HTTP/2 Enablement in Cloudflare (2026-06-30) · Jun 2026 · source · release history - Enables HTTP/2 on all ISC environments via Cloudflare, delivering improved security and performance over HTTP/1.1. Maintenance: HTTP/2 Enablement in Cloudflare (2026-06-30) · Jun 2026 · source · release history
Platform Event Data Retention shipped Provides a scheduled job to purge old event processing records from the database according to a configurable retention period.
Also counts toward: Scheduled jobs
release
- Adds an ISC Event Processing Table Cleaner job to purge old event records, with a default retention period of 7 days configurable via the Data Management Policy. Enhancement: ServiceNow Service Catalog v5.4 — Event-driven Approvals and Access Request Status Sync (2026-10-09) · Oct 2026 · source · release history
example
-
Configure the ISC Event Processing Table Cleaner retention window to match your company data policy.
In ServiceNow, navigate to the Data Management Policy for the ISC Event Processings table, activate the table cleaner rule, and set the retention period (default: 7 days) to your required value.Enhancement: ServiceNow Service Catalog v5.4 — Event-driven Approvals and Access Request Status Sync (2026-10-09) · Oct 2026 · source
UI Workflow Recording & Replay shipped Captures administrator UI interactions via a browser extension and replays them as automated provisioning, deprovisioning, and aggregation actions without custom scripting.
release
- Adds the SailPoint connectivity browser extension to record administrator UI workflows once and replay them for automated provisioning, deprovisioning, and aggregation against web apps that expose no API.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enhancement: Disconnected applications connector - limited availability (2026-10-09) · Oct 2026 · source · release history
- Enables zero-code connectivity by letting administrators map recorded UI inputs to SailPoint identity attributes (such as name or email) without writing custom scripts. Enhancement: Disconnected applications connector - limited availability (2026-10-09) · Oct 2026 · source · release history
GCP data classification ingestion for Data Access Security shipped Ingests classification tags already applied in Google Cloud onto the corresponding DAS assets, reusing existing GCP data classifications without re-running the DAS classification engine.
release
- Ingests classification tags already applied in Google Cloud onto the corresponding DAS assets, reusing existing GCP data classifications without re-classifying with the DAS engine. New Capability: Data Access Security - Google BigQuery Connector (2026-10-05) · Oct 2026 · source · release history
- Ingests existing Google Cloud classification tags onto corresponding DAS assets without using a new classification engine New Capability: Data Access Security - Google BigQuery Connector (2026-10-05) · Oct 2026 · source · release history
Governance Group Routing shipped Enables assigning a Governance Group to a source so that manual provisioning tasks are routed to all group members.
release
- Enables assigning a Governance Group to a source so that manual provisioning tasks are routed to all group members instead of a single owner, with ISC recording which individual member completed each task.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New Capability: Manual Task Support for Governance Groups (2026-09-25) · Sep 2026 · source · release history
- Adds support for assigning manual provisioning tasks to a source’s Governance Group New Capability: Manual Task Support for Governance Groups (2026-09-25) · Sep 2026 · source · release history
Certification Reporting Endpoint Migration shipped Migrates the certification reporting endpoint to a new location, requiring updates to existing API integrations.
release
-
The endpoint for extracting certification report data (CSV and PDF) via the
/campaign/and/certification/reporting flow is changing; existing API integrations that pull report data must be updated per the Certification Reports Endpoint Moving migration guidance. GA Announcement: Next Generation Certifications (2026-09-22) · Sep 2026 · source · release history - Certification report data retrieval endpoint is changing — migration guidance published at the Certification Reports Endpoint Moving resource. GA Announcement: Next Generation Certifications (2026-09-22) · Sep 2026 · source · release history
New Certification Email Templates shipped Introduces a new set of certification email templates alongside legacy ones, with automatic migration of templates and notification settings.
release
- Email notification templates larger than 133 KB will have images trimmed automatically during migration to fit the new v2 templating engine size limit. GA Announcement: Next Generation Certifications (2026-09-22) · Sep 2026 · source · release history
- Introduces a new certification email template set alongside the existing templates (labeled Legacy in the UI), enabling side-by-side comparison during migration. GA Announcement: Next Generation Certifications (2026-09-22) · Sep 2026 · source · release history
Dataset Resource Model for JDBC/REST shipped Enables the Dataset Resource model in JDBC and REST WebServices connectors to aggregate non-human identity entities.
release
- Enables the Dataset Resource model in JDBC and REST WebServices connectors to aggregate non-human identity (NHI) entities including Agent, MCP Server, and Tools SaaS Release Notes - September 11, 2026 · Sep 2026 · source · release history
- Introduces Datasets and Resources in SailPoint Agentic Fabric to group resources on a single aggregation schedule SaaS Release Notes - August 14, 2026 · Aug 2026 · source · release history
NetApp ONTAP mTLS Connectivity shipped Enables mutual TLS authentication for NetApp ONTAP integration sources.
release
- Adds mutual TLS (mTLS) authentication support for NetApp ONTAP connectivity, covering both client-side and server-side authentication.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ File Access Manager 8.5 Service Pack 2 Released! (2026-09-09) · Sep 2026 · source · release history
- Adds mutual TLS (mTLS) authentication support for NetApp ONTAP connectivity File Access Manager 8.5 Service Pack 2 Released! (2026-09-09) · Sep 2026 · source · release history
Data Segmentation for Human Identities shipped Restricts which human identities a scoped administrator can see, preventing cross-organisational identity data from leaking between admin roles.
release
- Enables delegated administration at subsidiary or team level without exposing cross-organizational identity data to scoped admins. Enhancement: Data Segmentation for Identities (2026-08-10) · Aug 2026 · source · release history
- Extends Data Segmentation to cover Human Identities, so administrators can restrict which identities a given user can see — not just Roles and Entitlements. Enhancement: Data Segmentation for Identities (2026-08-10) · Aug 2026 · source · release history
Deep Governance Connector Configuration shipped Provides a simplified Express Setup wizard for deploying and configuring Deep Governance connectors.
release
-
Adds displayName, status, and transformConfig attributes to
IDENTITY_PROFILE_UPDATEaudit events SaaS Release Notes - August 7, 2026 · Aug 2026 · source · release history - Adds Express Setup for configuring Deep Governance connectors in Identity Security Cloud, marked with an asterisk (*) on the connector list SaaS Release Notes - July 17, 2026 · Jul 2026 · source · release history
Shared Signals Framework Monitoring shipped Displays deployment health and activity metrics for Shared Signals Framework directly on the organizational dashboard.
release
- Adds MySailPoint home page widgets for tracking Shared Signals Framework transmitters and receivers. SaaS Release Notes - July 24, 2026 · Jul 2026 · source · release history
example
-
Monitor the health and activity of your Shared Signals Framework deployment directly from the MySailPoint dashboard.
In the MySailPoint home page, add the 'Shared Signals Framework' widget to a dashboard to view transmitter/receiver counts and event metrics.SaaS Release Notes - July 24, 2026 · Jul 2026 · source
SuccessFactors Connector Configuration shipped Extends the SuccessFactors connector to support multi-level nested OData schema attributes for user and employee data aggregation.
release
-
Expands Employee filter in
SAP SuccessFactorsconnector to include inactive external users SaaS Release Notes - July 17, 2026 · Jul 2026 · source · release history - SailPoint SuccessFactors connectors updated to support multi-level nested OData account schema attributes for user and employee data. SaaS Release Notes - June 12, 2026 · Jun 2026 · source · release history
BeyondTrust Password Safe Cloud PAM discovery connector shipped Discovers managed systems from BeyondTrust Password Safe Cloud on a continuous schedule so privileged assets stay current in the inventory.
Also counts toward: Scheduled jobs
release
- New BeyondTrust Password Safe Cloud PAM Discovery connector retrieves managed systems via the BeyondTrust public API using OAuth 2.0 client credentials, with support for continuous scheduled discovery. Expanding PAM application discovery: CyberArk Enhancement and New BeyondTrust & Delinea connectors (2026-07-09) · Jul 2026 · source · release history
example
-
Set up the new BeyondTrust Password Safe Cloud PAM Discovery connector to maintain a live inventory of managed systems in ISC.
In the ISC console, go to Admin > Connections > Discovery Connectors > Create Connector > PAM category > Configure next to "BeyondTrust Password Safe Cloud PAM".Expanding PAM application discovery: CyberArk Enhancement and New BeyondTrust & Delinea connectors (2026-07-09) · Jul 2026 · source
ISC API integration performance shipped Reduces the number of OAuth calls made during API integration operations to improve response times for connected systems.
release
- Reduces total OAuth calls to the Identity Security Cloud API, improving integration response times. Enhancement: ServiceNow Service Catalog for Identity Security Cloud v5.3 Released (2026-07-09) · Jul 2026 · source · release history
example
-
List all transforms in your tenant
sail transform list
Epic EMP Connector Configuration shipped Adds fine-grained block management parameters for Epic EMP connector account enablement and disablement workflows.
release
- Epic EMP connector adds disableRemoveBlockOnAccountEnable configuration parameter (default: false) to retain existing blocks when an account is enabled. SaaS Release Notes - June 12, 2026 · Jun 2026 · source · release history
- Epic EMP connector adds disableAddBlockOnAccountDisable configuration parameter (default: false) to not add blocks when an account is disabled. SaaS Release Notes - June 12, 2026 · Jun 2026 · source · release history
Email Template Editor shipped Provides an inline variable selector in the email template editor to dynamically insert and preview available attributes.
release
-
Enables inline variable selector for email templates by typing
${in the editor to view available template attributes. SaaS Release Notes - May 22, 2026 · May 2026 · source · release history
example
-
View available template attributes when customizing email templates directly in the editor.
Type '${' in the email template editor to open the inline variable selector.SaaS Release Notes - May 22, 2026 · May 2026 · source
Scoped Source Access Controls shipped Extends custom user levels to grant read-only visibility on specific sources, limiting operator and audit users to designated account data.
Also counts toward: Role-based access control
release
- Extends Custom User Levels to support Read Only permissions on Sources, letting admins grant scoped source visibility to operators, support, and audit users without full access.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enhancement: Custom User Level - Read Only Sources (2026-10-12) · Oct 2026 · source · release history
IAM Role Source Configuration Fields shipped Adds source configuration fields for IAM Role-based access including Role Name, Account ID, and Session details.
Also counts toward: Role-based access control
release
- Introduces new source configuration fields: Role Name, optional Account ID, optional External ID, Role Session Name, and Role Session Duration for IAM Role-based S3 access. Enhancement: Delimited File Connector - Securely Connect to AWS S3 Using IAM Role Authentication Instead of Long-Lived Access Keys (2026-10-05) · Oct 2026 · source · release history
CrowdStrike SecOps Identity Intelligence shipped Adds an Identity Security Intelligence panel to CrowdStrike Falcon detections for reviewing human and non-human identity context.
release
-
Adds the
SailPoint Identity Security Intelligence CrowdStrike Foundry appthat adds an Identity Security Intelligence panel to CrowdStrike Falcon Endpoint Security detections for reviewing human and non-human identity context. SaaS Release Notes - September 25, 2026 · Sep 2026 · source · release history
GitLab SaaS Identity Aggregation shipped Adds a GitLab SaaS connector to aggregate users, groups, projects, and discover non-human identities from GitLab instances.
release
-
Adds the
GitLab SaaSconnector for Identity Security Cloud to aggregate users, groups, projects, and discover non-human identities (tokens, bots, service accounts) fromGitLab.comand self-managed instances. SaaS Release Notes - September 25, 2026 · Sep 2026 · source · release history
Salesforce Secrets Discovery shipped Adds secrets and non-human identity discovery to the Salesforce SaaS connector.
release
- Adds Secrets and Non-Human Identity (NHI) discovery (Connected Apps, External Client Apps) and exposed credential detection across Salesforce objects in the Salesforce SaaS connector. SaaS Release Notes - September 25, 2026 · Sep 2026 · source · release history
UiPath Robotic Process Automation Connector shipped Adds a UiPath SaaS connector to aggregate robot accounts, groups, and discover machine identities via SailPoint Agentic Fabric.
release
-
Adds the
UiPath SaaSconnector for Identity Security Connectivity to aggregate robot accounts, groups, and discover machine identities via SailPoint Agentic Fabric. SaaS Release Notes - September 25, 2026 · Sep 2026 · source · release history
Workday Event Lite Delta Aggregation shipped Enables Event Lite transaction type support for delta aggregation in the Workday SaaS connector.
release
- Adds Event Lite transaction type support for delta aggregation in the Workday SaaS connector (requires enabling Delta Aggregation Lite Events and entering Event Lite Types). SaaS Release Notes - September 25, 2026 · Sep 2026 · source · release history
Enriched Campaign Filters shipped Provides enriched campaign filters as a replacement for unsupported combinations of search queries and campaign filters.
release
- Adds Enriched Campaign Filters (in-progress feature) to replace the unsupported combination of search queries and campaign filters on a single campaign. GA Announcement: Next Generation Certifications (2026-09-22) · Sep 2026 · source · release history
Access Request Item Sensitivity Labels shipped Displays effective privilege labels on access request cards to help users evaluate item sensitivity before submission.
release
-
Adds effective privilege labels (HIGH, MEDIUM, or LOW) on each access item card so requesters can evaluate sensitivity before adding items to a request.
New Capability: Next-Gen Access Request (2026-09-08) · Sep 2026
· source
· release history
gMSA Password Retrieval shipped Enables explicit configuration for automated retrieval of group Managed Service Account passwords to maintain continuous authentication.
example
-
Explicitly enable gMSA password retrieval so managed accounts that rely on gMSAPasswordData continue to function after the IQService-August-2026 upgrade.
IQService.exe -g --enable gMSAPasswordDataNew Capability: Integration Service (IQService-August-2026) is now LIVE! (2026-08-17) · Aug 2026 · source
Machine Account Discovery shipped Applies a machine learning model to detect and classify machine identities using expanded attribute analysis and ambiguity resolution.
Also counts toward: ML-based detection
release
- Enhances Machine Account Discovery learning model with broader attribute analysis, ambiguous account handling, and discovery explanations SaaS Release Notes - August 7, 2026 · Aug 2026 · source · release history
Identity Selector Filtering shipped Expands identity selector comparison operators to support mixed numeric type matching for granular filtering.
release
- Identity selector match criteria using GT, LT, GTE, and LTE operators now allow comparisons between mixed numeric types. SaaS Release Notes - June 12, 2026 · Jun 2026 · source · release history
Read-Only Source Configuration shipped Enables rapid setup of read-only connections for external sources to aggregate account data without full connector deployment.
example
-
Quickly configure read-only connections to new sources like Discord for account aggregation without full connector setup.
Go to Quick Compliance sources in Identity Security Cloud and select 'Discord' from the list of supported connectors.SaaS Release Notes - May 22, 2026 · May 2026 · source
User Notifications & Inbox shipped Provides a centralized notifications icon and inbox within the cyber tooling interface to aggregate user alerts and system messages.
release
- Adds a notifications icon and inbox to Identity Security Cloud. SaaS Release Notes - May 22, 2026 · May 2026 · source · release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
6 commands for SailPoint, each with where it came from. This tool has no source analysis yet, so there is no option reference and no captured run beside them.
No command matches.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for SailPoint, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail SailPoint puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Website history
sailpoint.com, every changeSailPoint's home page and 37 more pages as they looked each month from August 2021 to October 2026: 49 renders, 5 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Coverage
Missing something? Tell us
What SailPoint connects to, runs on and detects, read from its release notes and docs. So far: 7 new integrations, 1 new supported platform.
8 changes, tracked since Oct 3, 2026.
-
Oct 92026
new Disconnected applications connector
With SailPoint connectivity browser extension
SailPoint's disconnected applications connector treats the application's user interface as the integration layer. Instead of requiring an API, SailPoint learns how an administrator performs access tasks in the app's UI — then reliably replays those steps to automate identity lifecycle work.
-
Oct 52026
new Google BigQuery connector for Data Access Security
A SailPoint-built Google BigQuery connector brings BigQuery into DAS with crawl, permission collection, and classification ingest: Crawl / inventory of datasets, tables, views, and routines Permission collection - effective access, explained in enterprise identity terms for users, groups, and service accounts. Data classification ingestion from GCP - classification tags already applied in Google Cloud are ingested onto the corresponding DAS assets.
-
Oct 52026
new HashiCorp Vault (On-Premise) NHI Source Connector
This is a new ISC Source connector that discovers and aggregates non-human identities from on-premises HashiCorp Vault (Community version) into Identity Security Cloud.
-
Oct 52026
new SMB2/SMB3 with Kerberos authentication for Delimited File Connector
With Windows File Server, Samba
The SailPoint Delimited File Connector (VA-based) now supports SMB as a file transport. You can read identity files from Windows File Server and Samba (Linux) shares using Kerberos authentication.
-
Oct 32026
new File Access Manager Connector catalog documentation
Covers 25: Active Directory, SQL Server, Windows File Server, SharePoint, Exchange, NFS and 19 more
-
Oct 32026
new New connectors: Celigo, Eventzilla, FileCloud, Finch
-
Oct 32026
new Okta CIEM integration
**CSP Configuration** · Configuring AWS · Configuring Azure and Microsoft Entra ID · Configuring GCP · Configuring Okta
-
Oct 32026
new Okta as a supported identity provider for CIEM
## Supported Identity Providers - Azure AD - Okta
Identity & access 3
Cloud platforms & services 12
Databases & data platforms 6
Operating systems 1
Browsers & mobile 1
Other 12
Identity & access 1
Nothing first seen in this window. That doesn't mean SailPoint shipped nothing, only that we found no record of it.
How we count
Read from 10 of 104 release notes and docs updates we hold for SailPoint. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through SailPoint's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
104 entries
No entries match these filters.
- October 202621
- September 202624
- August 202620
- July 202624
- June 202612
- May 20263
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →