Socket is a commercial appsec platform that scans open source dependencies for vulnerabilities and malicious packages, giving supply chain visibility before risky code reaches production. It can be installed as a GitHub app that checks pull requests, run as a CLI or VS Code extension for local scanning, or deployed as Socket Firewall, which sits between package manager and registry to block malware at install time; a REST APIREST APIA web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. and JavaScript SDK cover custom workflows. It is built for developers and security teams who own dependency risk rather than network or endpoint defense, and its documentation cites use by projects like Next.js and Storybook alongside customers such as Vercel and Brave. Launched in 2021, it ships releases regularly, with the last one 42 days ago.
Socket is a security platform that detects and prevents supply chain attacks in open source dependencies and third-party code.
Which of my dependencies contain malicious or vulnerable code before it reaches production?
scans direct and transitive packages against Socket's intelligence and flags the ones with known vulnerabilities or malware, surfaced on pull requests before merge
Is a reported vulnerability actually exploitable in my application?
traces whether the vulnerable code path is reachable from the application's own call graph, distinguishing verdicts backed by human-verified specs from those inferred by AI-reviewed specs
Is a malicious package about to be installed on one of our machines?
sits between the package manager and the registry and checks every direct and transitive dependency against Socket's intelligence, blocking the install before the code lands
Did someone tamper with a package version after it was published?
shows the full commit history behind a package's tags on its registry page, with the commit currently associated with a force-pushed tag highlighted so a swapped reference stands out
Are the browser extensions our team installs secretly exfiltrating data or contacting attacker infrastructure?
continuously analyzes Chrome, Firefox, and Edge extensions for credential and clipboard theft, data exfiltration, remote payload loading, and changes in the domains they contact between releases
Which alerts need a person to act on them, and who is on the hook?
lets a policy route findings into rules that open tracked tickets in tools like Asana or ClickUp, with status kept in sync as the alert clears or the ticket closes
Built from Socket's releases, docs, README and our own runs.
“Seen” marks the month we first spotted a release the vendor didn't date.
Group names and tags are our labels.
+Comprehensive data export capabilitiesshippedProvides multiple export formats for security and compliance reporting, including CSV, JSON, PDF, CycloneDX SBOM, and license attribution details.23 releases · first seen Jul 2024▸
Shared capability: CycloneDX SBOM
release
23 total
Adds parsing of libs.versions.toml files during SBOM generation to improve dependency detection for Gradle projects without lockfiles.
Added Gradle Version Catalog Support for SBOM Generation · Apr 2026
· source
· release history
Adds aws_s3 bucket support for generic alert data export
Added Generic Bucket Export Integration · Feb 2026
· source
· release history
Adds csv, json, and parquet output format support for bucket exports
Added Generic Bucket Export Integration · Feb 2026
· source
· release history
Adds azure_blob_storage bucket support for generic alert data export
Added Generic Bucket Export Integration · Feb 2026
· source
· release history
Adds google_cloud_storage (GCS) bucket support for generic alert data export
Added Generic Bucket Export Integration · Feb 2026
· source
· release history
Adds openvex_bom method for exporting Software Bill of Materials in OpenVEX format
Python SDK: Expanded Endpoint Coverage and Enhancements · Jan 2026
· source
· release history
+Ruby ecosystem scanningshippedExtends dependency scanning to Ruby ecosystems, automatically detecting vulnerabilities and supply chain risks in Ruby projects.1 release · first seen Apr 2025▸
Shared capability: Dependency scanning
release
Enables Ruby scanning by default for all users
Rubygems Ecosystem Support Now Generally Available · Apr 2025
· source
· release history
+Dependency scanningshippedScans manifest files to detect dependency changes and vulnerabilities, and lists scan history for an organization.45 releases · 6 other sources · first seen Jun 2024▸
Adds Socket for Origin integration in the Origin App Marketplace, enabling automatic dependency scans on Origin pull requests when opened or new commits are pushed.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
announced · Oct 2026
· source
· release history
Scans supported manifests and lockfiles — including dependency changes in monorepo workspaces — by comparing the target branch with Origin's proposed merge result.
announced · Oct 2026
· source
· release history
Posts a Socket Security / Dependency scan check on Origin pull requests, showing scan progress, a policy-based verdict, and a link to the full report — with a rerun button directly in Origin.
announced · Oct 2026
· source
· release history
Posts PR comments with dependency overviews, scores, severity labels, and report links, updating automatically as the PR changes.
announced · Oct 2026
· source
· release history
POST /v0/orgs/{org_slug}/diff-scans/from-ids returns a 302 Found response with a Location header pointing to the existing diff scan when on_duplicate=redirect is set and a duplicate scan exists
Add duplicate redirect support to diff scan creation · May 2026
· source
· release history
Adds created-date filtering with custom calendar options and before/after operators to the Scans page
Add relative date filters to Vulnerabilities and Scans · May 2026
· source
· release history
docs
15.12.9 (Oct 16. 2026) now updates yarn that pin a vulnerable version, and skips only the fix it can't apply in a yarn project instead of failing the whole project. Skipped fixes are listed under notApplied failing with EOVERRIDE on npm projects whose pin one of their own direct dependencies.
seen Oct 2026
· source
15.12.1 (Oct 6. 2026) supports components that attribute dependencies to their subprojects' build files. 15.12.0 (Oct 6. 2026) can now write a scoped override or resolution when a parent's version range is the only thing blocking a fix.
docs update · Oct 2026
· source
example
Connect Socket to Origin so every pull request automatically gets dependency security checks without leaving your Origin workflow.$ In the Origin App Marketplace, find Socket, click Install, authorize your Socket organization, and confirm the connection.
announced · Oct 2026
· source
List the scans for the organization.$ socket scan list
Create a new dependency scan from manifest files in the current dir.$ socket scan create ./
Show package changes between two scans.$ socket scan diff <SCAN_ID1> <SCAN_ID2>
+Unified security workflowshippedCombines SAST for 14 programming languages, secrets detection, container/Dockerfile scanning, and CVE scanning into a single workflow.1 release · 3 other sources · first seen Oct 2025▸
Shared capability: Vulnerability scanning
release
Unifies Static analysis (SAST) for 14 programming languages, Secrets detection, Container/Dockerfile scanning, and CVE scanning under one workflow
New: Socket Basics · Oct 2025
· source
· release history
docs
Firefox add-ons Gradle is fully supported. The recommended setup is to generate a Socket facts file with socket manifest gradle ; committing a is supported if you prefer not to run the CLI. Gradle is fully supported.
seen Aug 2026
· source
✅‡ ✅‡ ✅‡ ‡ Note: For JVM projects these requirements follow the build tool, not the language. A generated SBOM is required for sbt, and for Gradle unless the project commits a gradle.lockfile or a libs.versions.toml version catalog; for Maven, Socket reads directly.
seen Aug 2026
· source
covers the build in the directory you run it from. If your repository contains several independent Gradle builds, run socket manifest dynamic-sbom-inference instead to generate a Socket facts file for each of them (see Multiple builds ). socket scan create --reach--dynamic-sbom-inference .
seen Aug 2026
· source
+Other / not yet classified43 featuresFeatures we have not matched to a capability yet. A suggested match is marked.▸
+Enhanced CLI and API usabilityshippedExpands CLI commands for scan management, threat feeds, and repository operations, while improving API parameters for filtering and metadata handling.56 releases · 2 other sources · first seen Jun 2024▸
Also counts toward: Administrative audit log, Command-line interface
release
56 total
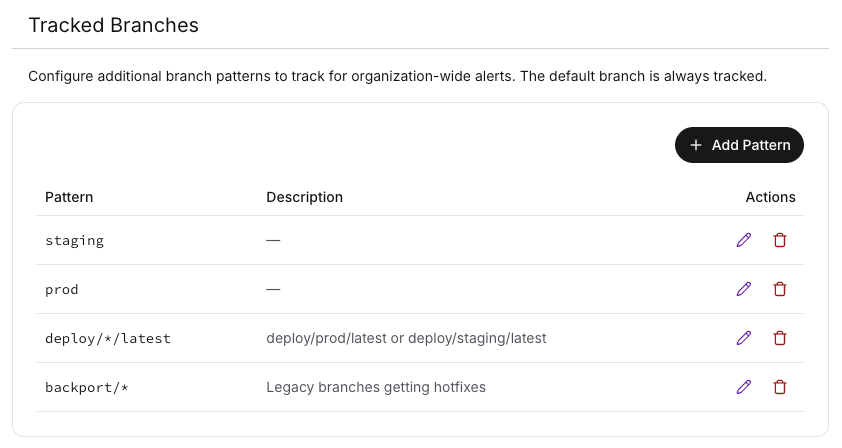
API users can now track non-default branches by setting the branch and set_as_pending_head fields when creating a full scan.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Organization alerts can now track multiple branches (2026-11-02) · Nov 2026
· source
· release history
Migrate report view calls from the deprecated GET /v0/report/view/{id} endpoint to GET /v0/orgs/{org_slug}/full-scans/{full_scan_id} before November 20, 2026 — the old endpoint now advertises its retirement in a Sunset response header.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
changelog · Oct 2026
· source
· release history
The GET /v0/report/view/{id} endpoint is retired on November 20, 2026; integrations using it must switch to GET /v0/orgs/{org_slug}/full-scans/{full_scan_id}.
changelog · Oct 2026
· source
· release history
Omitting the workspace parameter now correctly targets the default-workspace repository for full or diff scans
Fixed Empty Workspace Parameter Handling for Repository Scans · Feb 2026
· source
· release history
Adds publishedAt field to Threat Feed API responses (ISO 8601 or null)
PublishedAt Field Added to Threat Feed API · Jan 2026
· source
· release history
Adds the ability to override the default User Agent string in the Socket Python SDK.
Python SDK: Custom User Agent Support · Jan 2026
· source
· release history
example
Check the new full-scans endpoint to retrieve a scan report after the old view endpoint is retired.$ curl -s -H 'Authorization: Bearer <token>' 'https://api.socket.dev/v0/orgs/<org_slug>/full-scans/<full_scan_id>'
changelog · Oct 2026
· source
Verify the Sunset header on the deprecated endpoint before your migration deadline to confirm the retirement date.$ curl -sI -H 'Authorization: Bearer <token>' 'https://api.socket.dev/v0/report/view/<id>' | grep -i sunset
changelog · Oct 2026
· source
+Real-time analytics and dashboard visibilityshippedEnhances the dashboard with aggregated metrics, filtered data views, and real-time alert statistics to provide immediate insights into organizational security posture.55 releases · first seen Aug 2024▸
release
55 total
Organization-wide alerts now track multiple branches per repository (up to 5), with alerts broken down by label, repository, and branch in the dashboard.
Organization alerts can now track multiple branches (2026-11-02) · Nov 2026
· source
· release history
Private packages that Socket cannot score now display N/A instead of a numeric score in pull request comments and dependency views.
Private Package Scores Now Display as N/A (2026-07-03) · Jul 2026
· source
· release history
Connects package findings to affected repositories and organization alerts
Socket MCP adds organization alerts, threat feed, and package inspection · Jun 2026
· source
· release history
Adds organization-level alert review with filtering by severity or repository
Socket MCP adds organization alerts, threat feed, and package inspection · Jun 2026
· source
· release history
Supports relative date presets like 1 week ago and 1 month ago on Vulnerabilities and Scans pages
Add relative date filters to Vulnerabilities and Scans · May 2026
· source
· release history
Adds a Detected date filter specifically for the Vulnerabilities page
Add relative date filters to Vulnerabilities and Scans · May 2026
· source
· release history
+Granular security policy configurationshippedAllows users to define specific alert severities and enforcement actions (Block, Warn, Monitor, Ignore) via custom profiles to manage CI/CD flow and reduce noise.35 releases · 12 other sources · first seen Jul 2024▸
Also counts toward: CI/CD pipeline integration, REST API
release
35 total
New Asana integration lets teams create and manage Asana tasks from Socket alerts, either manually or via ticketing rules that filter by event, type, priority, and repository — with configurable sync between task and alert status; available in beta on Business and Enterprise plans.
changelog · Aug 2026
· source
· release history
Supports ticketing rules that filter alerts by event, type, priority, repository, and other attributes to automate Asana task creation.
New: Asana integration for alert ticketing (2026-08-25) · Aug 2026
· source
· release history
Allows configuring Asana workspace, project, tags, and assignee per ticketing rule, with bi-directional status sync between linked tasks and alerts.
New: Asana integration for alert ticketing (2026-08-25) · Aug 2026
· source
· release history
Adds a Create Ticket button on any Socket alert to manually create a linked Asana task — selecting workspace, project, tags, and assignee — with a bidirectional link between the alert and the task.
announced · Aug 2026
· source
· release history
New Settings → Integrations → Asana UI in the Socket dashboard lets an Owner or Admin connect one or more Asana workspaces via OAuth, with no separate app to install.
announced · Aug 2026
· source
· release history
Two-way sync keeps Asana tasks and Socket alerts current: Socket can mark an Asana task complete when an alert clears, and completing the Asana task can triage-ignore the linked Socket alert.
announced · Aug 2026
· source
· release history
docs
10 total
GET /v0/orgs/{org_slug}/alert-policies/migration/status returns where your organization is in the migration to Policies. It tells you when policy and rule writes start working, when the legacy writes stop, and which configuration is deciding your alerts right now. The endpoint is read-only.
docs update · Sep 2026
· source
If you already POST Alert Triage rules, this endpoint converts those request bodies. POST /orgs/{org_slug}/alert-policies/migration/translate takes the same alertTriage array you send to POST /orgs/{org_slug}/triage/alerts and returns the new alert-resolution or policy-rule requests. Nothing is created.
docs update · Sep 2026
· source
While your organization is previewing the migration to Policies, real policy and rule writes return 409 until you confirm the migration. ?dry_run=true tries the same write and returns 200 . Nothing is saved. Reading the policy API is not a preview of the converted configuration. That preview is in the dashboard.
docs update · Sep 2026
· source
If you already POST Alert Triage rules to ignore alerts, use Translating Alert Triage Payloads to convert those request bodies into resolutions. Add ?dry_run=true to that POST to check it without saving anything. Translating Alert Triage Payloads — convert an ignored triage rule into a resolution.
docs update · Sep 2026
· source
Add ?dry_run=true to a policy, rule, or resolution write to check the request without saving anything. A dry-run returns the same body that a normal write would return. Socket does not create, update, or delete the policy, rule, or resolution, and matching alerts stay on the open list.
docs update · Sep 2026
· source
A policy rule matches on facts about the alert, grouped into three families: Location — where the dependency was found: which repository, which manifest file. Artifact — the package itself: ecosystem, name, namespace, version, publication date, and Socket's health scores.
seen Aug 2026
· source
example
Set up an automated ticketing rule to route high-priority supply chain alerts directly to the right Asana project without manual triage.$ In the Socket dashboard, go to Settings → Integrations → Asana → ticketing rules. Step 1: select the alert events that trigger the rule.
announced · Aug 2026
· source
Connect an Asana workspace to your Socket organization so alerts can be routed as trackable tasks.$ In the Socket dashboard, go to Settings → Integrations → Asana and click Connect. Authorize via OAuth — no third-party admin console required.
announced · Aug 2026
· source
+Reachability analysisshippedsuggestedProduces reachability verdicts for vulnerabilities during alert scans, optionally extending coverage via AI-generated specifications beyond human-verified ones.25 releases · 12 other sources · first seen Apr 2025▸
Suggested capability: Vulnerability prioritization. This is our guess, not confirmed.
release
25 total
PHP and Composer support promoted from Experimental to Beta and now available to all Socket users; PHP reachability analysis is generally available for Team plan customers and above without requiring Experimental access.
changelog · Aug 2026
· source
· release history
PHP reachability analysis is now generally available for Team plan customers and above, with no Experimental access required — includes precomputed reachability and full application reachability.
PHP and Composer support is now in beta (2026-08-21) · Aug 2026
· source
· release history
PHP reachability analysis is now generally available for customers on Team plans and higher
PHP and Composer support is now in beta (2026-08-21) · Aug 2026
· source
· release history
Repository-scoped API tokens can now retrieve the supported-files list required to start reachability scans
Repository-Scoped API Tokens Now Support Reachability Scans (2026-07-09) · Jul 2026
· source
· release history
Adds a Specification field to Alert details showing whether the reachability result came from an AI-generated or human-verified specification
New: AI-Reviewed Reachability Specifications · Jun 2026
· source
· release history
New Specification field in alert details surfaces whether a reachability result was produced by an AI-generated or human-verified specification.
New: AI-Reviewed Reachability Specifications (2026-06-30) · Jun 2026
· source
· release history
docs
10 total
15.12.3 (Oct 9. 2026) Recognise Socket facts files with any *.socket.facts.json name (e.g. pom.xml.socket.facts.json ) in Soundness and memory usage improvements for the Python reachability analysis. More precise modeling of PyTorch prevents analysis blow-ups in projects that use it. 15.12.2 (Oct 7.
docs update · Oct 2026
· source
15.12.2 (Oct 7. 2026) Fixed reachability analysis reporting every vulnerability as unreachable in bun workspaces installed with bun's isolated linker.
docs update · Oct 2026
· source
15.11.6 (Oct 2. 2026) Performance, recall and out-of-memory handling improvements for the JavaScript/TypeScript, PHP and JVM reachability analyses. Socket Fix (NuGet): when the upgrades make dotnet restore fail, they are now undone and reported with NuGet's reason, instead of leaving the project failing restore.
docs update · Oct 2026
· source
15.10.54 (Sep 24. 2026) Fix a stack overflow in the Ruby reachability analysis. 15.10.53 (Sep 24. 2026) Fix npm workspace scans failing to install the project's own workspace packages. 15.10.52 (Sep 24.
docs update · Sep 2026
· source
15.10.46 (Sep 18. 2026) Fix a crash when analyzing a function with defer inside a range-over-func loop in the Go reachability analysis. 15.10.45 (Sep 17. 2026) Model calls to pickle.{Pickler,Unpickler} hooks through load dump in the Python reachability analysis. 15.10.44 (Sep 17.
docs update · Sep 2026
· source
15.10.41 (Sep 14. 2026) Performance and memory usage improvements for the Python reachability analysis. 15.10.40 (Sep 11. 2026) Support pnpm 12 and newer, whose can contain more than one YAML document. 15.10.39 (Sep 8. 2026) Internal changes to how analysis timeouts are classified. 2 days ago
seen Sep 2026
· source
example
Enable AI-generated reachability specs org-wide to get reachability verdicts on a broader set of vulnerabilities during alert scans.$ In the console, go to Settings → Alert Scans → Reachability and enable the AI-generated reachability specifications option.
New: AI-Reviewed Reachability Specifications (2026-06-30) · Jun 2026
· source
Run a scan focusing only on exploitable reachability in supported languages to filter out irrelevant CVEs.$ socket scan create --reach
Tier 1 Reachability Now Available for Enterprise Teams · Sep 2025
· source
+Multi-organization managementshippedLets users switch between, search across, and manage multiple organizations from a unified view.18 releases · 1 other source · first seen Jun 2024▸
Also counts toward: Multi-tenant management
release
18 total
Organization settings are now accessible directly from the Settings link at the bottom of the dashboard sidebar.
changelog · Oct 2026
· source
· release history
Adds a searchable All organizations view in the Organization Switcher for users with multiple organizations
Redesigned Organization Switcher for Faster Navigation · Jun 2026
· source
· release history
New searchable All Organizations view for users belonging to multiple organizations.
Redesigned Organization Switcher for Faster Navigation (2026-06-29) · Jun 2026
· source
· release history
Surfaces Settings and organization list up front in the redesigned switcher UI
Redesigned Organization Switcher for Faster Navigation · Jun 2026
· source
· release history
Redesigned organization switcher surfaces Settings and organizations at the top level for faster access.
Redesigned Organization Switcher for Faster Navigation (2026-06-29) · Jun 2026
· source
· release history
Supports deployment through editor configuration, DNS override, or enterprise egress forwarding.
New: Socket Firewall support for VS Code and Open VSX · Jun 2026
· source
· release history
example
Quickly jump between organizations when managing multiple clients or teams.$ In the Socket console, click the organization switcher in the top navigation, then type an organization name in the All Organizations search box to filter and select it instantly.
Redesigned Organization Switcher for Faster Navigation (2026-06-29) · Jun 2026
· source
+Expanded threat intelligence and detectionshippedBroadens threat detection scope across multiple ecosystems (PyPI, Go, Maven) and introduces specific high-severity alerts for supply chain risks like suspicious GitHub stars.14 releases · first seen Aug 2024▸
Also counts toward: Command-line interface, JSON data export
release
14 total
Enables querying the Socket threat feed by ecosystem, category, and time window
Socket MCP adds organization alerts, threat feed, and package inspection · Jun 2026
· source
· release history
Supports authentication for org alerts and threat feed; depscore remains public
Socket MCP adds organization alerts, threat feed, and package inspection · Jun 2026
· source
· release history
Exposes new timestamp in GET /v0/orgs/{org_slug}/threat-feed endpoint
PublishedAt Field Added to Threat Feed API · Jan 2026
· source
· release history
Adds a new Debug Webhook view showing a paginated table of sent messages with detailed request/response delivery logs
New: Webhook Testing and Debugging · Dec 2025
· source
· release history
Adds socket webhook events that fire when an alert is created, updated, or cleared across repositories
New: Webhook Events for Alert Changes · Nov 2025
· source
· release history
Adds create, get, list, update, and delete API endpoints for managing webhooks in Socket API v0
API Support for Managing Webhooks · Nov 2025
· source
· release history
+Multi-ecosystem package resolution improvementsshippedImproves dependency accuracy by enhancing Yarn lockfile parsing, supporting multi-package workspaces, and enabling direct linking to external module sources.12 releases · first seen Oct 2024▸
release
12 total
Allows listing, reading, and searching published package artifacts without local installation
Socket MCP adds organization alerts, threat feed, and package inspection · Jun 2026
· source
· release history
Adds Manifest Alerts view to scan results for detecting missing lockfiles in application and project repositories
New: Manifest Alerts for missing lockfiles · Jun 2026
· source
· release history
Supply chain attack campaign descriptions now support Markdown formatting (bold text, links, lists, code blocks) across both public and dashboard views.
Added Markdown Rendering for Supply Chain Attack Descriptions · Mar 2026
· source
· release history
Alert details pages now display associated files for alerts such as obfuscated code, native code, and eval usage
Improved Alert Details With Associated Files · Jan 2026
· source
· release history
Adds Slack bot mode to the Socket Python CLI alongside existing webhook-based notifications
Python CLI: Slack Bot Mode Support Added · Jan 2026
· source
· release history
Adds accurate semantic version detection and comparison specifically for Python packages
New: PyPI Version Diff Support · Sep 2025
· source
· release history
+Expanded ecosystem visibilityshippedDisplays additional context like publisher details, keywords, download trends, and deprecation status across non-native package ecosystems to improve evaluation.11 releases · first seen Jan 2026▸
release
11 total
Closes cross-store coverage gap by pairing Chrome Web Store analysis (including Chrome extensions Edge users can install) with new Microsoft Edge Add-ons analysis.
announced · Aug 2026
· source
· release history
Adds a daily downloads chart to Packagist package pages to show adoption over time.
Packagist Package Pages Now Show Daily Download Trends · Jun 2026
· source
· release history
Daily download trends visualization is added to crate package pages for adoption analysis
Crates Package Pages Now Show Daily Download Trends · Jun 2026
· source
· release history
Crates package pages on Socket.dev now include daily download metrics sourced from crates.io
Crates Package Pages Now Show Daily Download Trends · Jun 2026
· source
· release history
Adds a warning banner on Go and PyPI package pages when a version is retracted or yanked
Surface Go retraction and PyPI yank warnings · Jun 2026
· source
· release history
Displays package keywords on GitHub Actions and Packagist package pages to provide more context.
Surface package keywords for GitHub Actions and Packagist · Jun 2026
· source
· release history
+Browser extension telemetry and controlsshippedProvides real-time threat metrics within the browser extension and adds controls to reset accumulated statistics for user privacy and session management.8 releases · first seen Aug 2024▸
release
8 total
Introduces a new dashboard settings page for admins and owners to enable or disable telemetry at the organization level
Org-level Telemetry Configuration · Nov 2025
· source
· release history
Adds experimental scanning capability for OpenVSX extensions
New: OpenVSX Extension Scanning · Nov 2025
· source
· release history
Adds GET /api/telemetry and PUT /api/telemetry endpoints to retrieve and update org-level telemetry settings
Org-level Telemetry Configuration · Nov 2025
· source
· release history
Adds AI-detected possible typosquat alert to distinguish AI-flagged typosquat threats from human-reviewed ones
Introducing a New "AI-Detected Possible Typosquat" Alert · Dec 2024
· source
· release history
Generates Known Malware alerts for npm security holding packages (empty placeholders for removed packages) to indicate original packages were likely malicious.
npm Security Holding Packages Now Flagged as Known Malware · Nov 2024
· source
· release history
Adds full Go package threat detection and security metrics in the Socket Web Extension for Chrome and Firefox
Web Extension Now Supports Go · Nov 2024
· source
· release history
+Microsoft Teams notificationsshippedRoutes organization alerts and campaign notifications to Microsoft Teams channels via webhooks, supporting digest grouping and structured Adaptive Cards.5 releases · 2 other sources · first seen Sep 2026▸
Also counts toward: Outbound webhooks (the product notifies you)
release
Groups related alert activity into digests before posting to Teams, preventing channel flooding when a scan surfaces many alerts at once.
announced · Sep 2026
· source
· release history
Attack campaign notifications indicate whether affected packages are present in the organization — showing impacted repositories or confirming no monitored repositories are affected — without requiring manual per-repository checks.
announced · Sep 2026
· source
· release history
New subscription model lets owners and admins route organization alerts and supply chain attack campaign notifications to specific Teams channels, filtered by alert category (supply chain risk, vulnerability, quality, maintenance, license), severity, Socket priority, repository, or package ecosystem.
announced · Sep 2026
· source
· release history
Delivers notifications as structured Adaptive Cards summarizing alert totals by severity, affected repository count, individual finding previews, and a direct link to the Socket dashboard.
announced · Sep 2026
· source
· release history
Adds Microsoft Teams as a notification destination in Settings → Integrations → Notifications, configured via a Microsoft Workflows incoming webhook (HTTP POST URL) alongside the existing email channel.
announced · Sep 2026
· source
· release history
example
Connect a Teams channel to Socket so critical supply chain alerts land in your security team's channel automatically.$ In Socket, go to Settings → Integrations → Notifications → Create Channel, select 'Microsoft Teams', enter a channel name, and paste the HTTP POST URL copied from your Microsoft Workflows 'Post to a…
announced · Sep 2026
· source
Route only critical supply chain risk alerts for a specific repository to a dedicated engineering Teams channel, keeping noise out of the general security channel.$ In Socket, go to Settings → Integrations → Notifications → Create Subscription, choose the 'alert created' event, set filters to category: 'supply chain risk', severity: critical, and the target…
announced · Sep 2026
· source
+Firefox extension scanningshippedScans Firefox extensions from Mozilla's official add-ons directory for malware, credential theft, data exfiltration, remote loading, obfuscation, impersonation, and permission or code changes.7 releases · first seen Aug 2026▸
release
7 total
New Firefox extension scanning covers every extension in Mozilla's official add-ons directory, monitoring for permission changes, network activity, malware, credential and clipboard theft, data exfiltration, remote loading, obfuscation, and impersonation; available in Experimental for Enterprise customers.
changelog · Aug 2026
· source
· release history
Scans every Firefox extension listed in Mozilla's official add-ons directory, monitoring new releases for changes in permissions, code, network activity, and behavior.
New: Firefox extension protection (2026-08-20) · Aug 2026
· source
· release history
Adds Firefox extension protection capability scanning extensions from Mozilla's official add-ons directory for permissions, code changes, network activity, and behavior anomalies
New: Firefox extension protection (2026-08-20) · Aug 2026
· source
· release history
Enables monitoring of new Firefox extension releases for changes in permissions, code, network activity, and behavior.
New: Firefox extension protection · Aug 2026
· source
· release history
Adds support for scanning Firefox extensions listed in Mozilla's official add-ons directory.
New: Firefox extension protection · Aug 2026
· source
· release history
Detects malware, credential and clipboard theft, data exfiltration, remote loading, obfuscation, impersonation, and related campaign activity in Firefox extensions.
New: Firefox extension protection (2026-08-20) · Aug 2026
· source
· release history
+Repository label managementshippedAllows users to assign custom labels to repositories for grouping and manage those labels through the dashboard or API.7 releases · first seen Apr 2025▸
Also counts toward: REST API
release
7 total
Adds label selection in RepoSwitcher dropdown to filter repositories across the entire dashboard
Filter by Repository Labels in RepoSwitcher · Sep 2025
· source
· release history
Introduces new, simplified label management for repositories.
Reintroduced Repository Page with Improved Label Management · Sep 2025
· source
· release history
Adds PUT method on the label endpoint to rename repository labels via API
New: Rename Repository Labels via API · Jun 2025
· source
· release history
Adds association capabilities to link or unlink labels with alerts via the SDK
Python SDK: Added Support for Historical and Label Endpoints · Jun 2025
· source
· release history
Adds labels/settings endpoints allowing get, update, and delete configuration for specific labels
Python SDK: Added Support for Historical and Label Endpoints · Jun 2025
· source
· release history
Enables filter, sort, and search functionality based on repository labels
New: Repository Labels + Security Policies · Apr 2025
· source
· release history
+ClickUp integrationshippedRoutesso alerts to ClickUp tasks via manual creation or automated rules with bi-directional status sync between Socket findings and ClickUp workspaces.5 releases · 1 other source · first seen Aug 2026▸
Also counts toward: Ticketing integration
release
New ClickUp integration (beta) lets teams create ClickUp tasks from Socket alerts via Settings → Integrations → ClickUp in the Socket dashboard.
announced · Aug 2026
· source
· release history
Manual task creation available for individual alerts via the Create Ticket button in the Socket alert view, with selection of target ClickUp Workspace and List (displayed with full Space / List or Space / Folder / List path).
announced · Aug 2026
· source
· release history
Bi-directional status sync keeps Socket alerts and ClickUp tasks updated: clearing an alert can move the linked task to completed, and closing or completing a task in ClickUp can triage-ignore the corresponding Socket alert.
announced · Aug 2026
· source
· release history
Automated ticketing rules route matching Socket findings into a chosen ClickUp Workspace and List, with configurable priority (Urgent, High, Normal, Low, or Auto to map Socket priority automatically), tags, and assignee.
announced · Aug 2026
· source
· release history
ClickUp task updates, status changes, and deletions are delivered to Socket via Workspace webhooks, giving security monitors and engineers a shared view of issue status.
announced · Aug 2026
· source
· release history
example
Set up the ClickUp integration in Socket to start routing alerts as tasks into your team's existing ClickUp workflows.$ In the Socket dashboard, go to Settings → Integrations → ClickUp and click Connect.
announced · Aug 2026
· source
+Python dependency fixingshippedAutomatically fixes vulnerabilities in Python projects by upgrading affected dependencies in requirements.txt and uv.lock files.5 releases · 1 other source · first seen Apr 2025▸
Also counts toward: Scripting language support, Ticketing integration
release
Adds Asana integration (beta, Business and Enterprise plans) to create and manage Asana tasks directly from Socket alerts.
New: Asana integration for alert ticketing (2026-08-25) · Aug 2026
· source
· release history
Adds --no-major-updates flag to prevent major version upgrades during remediation
Socket CLI 1.1.24–1.1.25 · Oct 2025
· source
· release history
socket fix now supports automatically fixing vulnerabilities in Python (PyPI) projects by upgrading affected dependencies in requirements.txt and uv.lock files.
New: Support for Python Vulnerability Fixes in socket fix · Oct 2025
· source
· release history
Adds --only-compute flag to socket fix to compute fixes without applying them
Socket CLI v1.1.13–v1.1.15 · Sep 2025
· source
· release history
Adds --autopilot mode for automated testing and merging in CI
New: Socket Fix for Safe, Automated Dependency Upgrades · Apr 2025
· source
· release history
example
Validate dependency upgrades safely by running the test suite before applying changes.$ socket fix --test
New: Socket Fix for Safe, Automated Dependency Upgrades · Apr 2025
· source
+Edge extension scanningshippedContinuously analyzes Microsoft Edge Add-ons for malware, credential theft, data exfiltration, remote code loading, obfuscation, impersonation, and version changes.4 releases · 1 other source · first seen Aug 2026▸
release
Connects related extensions across stores through reused code, shared infrastructure, publisher patterns, and coordinated campaigns.
announced · Aug 2026
· source
· release history
Identifies command-and-control infrastructure, suspicious endpoints, remote payload sources, and changes in domains contacted by Edge extensions.
announced · Aug 2026
· source
· release history
Adds continuous analysis of extensions published through Microsoft Edge Add-ons, covering malware, credential and clipboard theft, data exfiltration, remote code loading, obfuscation, and impersonation — the same detections previously available for Chrome and Firefox.
announced · Aug 2026
· source
· release history
Enables version-change comparison for Edge extensions, surfacing meaningful differences in code, permissions, network activity, and behavior between releases under the same extension identity.
announced · Aug 2026
· source
· release history
example
Enable Edge extension coverage for your enterprise org — reach out to your Socket account team or contact Socket to get started with the Experimental rollout.$ In the Socket dashboard, contact your Socket account team to enable Edge coverage under the Experimental tier for your enterprise organization.
announced · Aug 2026
· source
+Firewall telemetry data exportshippedRoutes Socket Firewall event logs to external SIEMs or data pipelines for retention and analysis.4 releases · 1 other source · first seen Feb 2025▸
Also counts toward: SIEM forwarding
release
Adds UI path Settings > Data Export > Create Integration for exporting Socket Firewall telemetry events
Add Firewall events data export · Jun 2026
· source
· release history
Enables export of Socket Firewall telemetry event logs to external data sources through a new Data Export integration.
Add Firewall events data export (2026-06-16) · Jun 2026
· source
· release history
Firewall event details include a Copy JSON button to copy the full event body.
Add security policy confirmations and JSON copy actions in the dashboard · Apr 2026
· source
· release history
Adds Microsoft Sentinel as a destination for Socket Health report alerts via the Socket SIEM Connector
New Integration: Microsoft Sentinel Support Added to Socket SIEM Connector · Feb 2025
· source
· release history
example
Route Firewall event logs to an external SIEM or data pipeline for retention and analysis.$ In the console, go to Settings > Data Export > Create Integration, then select "Telemetry events" as the data type.
Add Firewall events data export (2026-06-16) · Jun 2026
· source
+Malware campaign impact analysisshippedShows per-organization impact summaries for known malware campaigns — whether packages were blocked, detected, or missed — with drill-down into affected packages, versions, repositories, branches, and linked scan reports or Firewall events.3 releases · 1 other source · first seen Oct 2026▸
release
New Org Impact tab on each campaign shows each affected package and version separately, with the repositories, branches, and first/last-seen dates that link directly to the originating scan report or matching Socket Firewall events.
announced · Oct 2026
· source
· release history
Adds per-organization campaign impact summaries — Blocked by Socket, Detected in Firewall/SCA, or Not Detected — to every malware campaign on the Threat Intel → Campaigns page, drawn from repository scans and Firewall event traffic.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
announced · Oct 2026
· source
· release history
Adds Blog and Affected Packages tabs to each campaign detail view, surfacing Socket write-ups and the complete list of affected packages alongside the impact data.
announced · Oct 2026
· source
· release history
example
Determine whether a newly publicized malware campaign reached your org and whether Socket blocked or only detected it, then trace every affected repository and branch to the exact scan.$ In the Socket dashboard, go to Threat Intel → Campaigns. Locate the campaign in question and check the org-level status badge (Blocked by Socket, Detected in Firewall/SCA, or Not Detected).
announced · Oct 2026
· source
+OAuth token scope and role validationshippedValidates OAuth token requests against both the token's granted scopes and the requester's current role or service-account permissions at request time.4 releases · first seen Oct 2026▸
Also counts toward: Role-based access control
release
Adds current-role checks for OAuth requests so that role changes take effect on the next request, including for linked service-account requests.
changelog · Oct 2026
· source
· release history
Adds repository access checks before computing or returning fixes for user OAuth sessions governed by repository or workspace policies, returning 403 for unfiltered repository endpoints.
changelog · Oct 2026
· source
· release history
For organizations with current-role checks enabled, OAuth token requests now validate both the token's granted scopes and the user's current role permissions, with role changes taking effect on the next request.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
OAuth access stays in sync with role changes (2026-10-15) · Oct 2026
· source
· release history
Linked service-account OAuth requests now check current service-account permissions alongside granted token scopes.
OAuth access stays in sync with role changes (2026-10-15) · Oct 2026
· source
· release history
+Multi-channel alert routingshippedRoutes security and compliance alerts to external platforms via configurable channels and webhooks.4 releases · first seen Oct 2025▸
Also counts toward: Ticketing integration, Outbound webhooks (the product notifies you)
release
New integration with Asana for alert ticketing.
New: Asana integration for alert ticketing · Aug 2026
· source
· release history
Enables posting alerts to multiple Slack channels using a bot token
Python CLI: Slack Bot Mode Support Added · Jan 2026
· source
· release history
Supports configurable filters per channel
Python CLI: Slack Bot Mode Support Added · Jan 2026
· source
· release history
Integrates 12 notification channels (Slack, Jira, GitHub, Microsoft Teams) via config settings
Expanded: Socket Basics Configuration · Oct 2025
· source
· release history
+Vulnerability alert CSV exportshippedExports vulnerability alerts to CSV, including human-readable alert titles for direct CVE identification and consistently populated upgrade version values.4 releases · first seen Sep 2025▸
Also counts toward: CSV data export
release
CSV exports now include a human-readable Alert Title column for vulnerability alerts
Alert Titles Added to CSV Exports · Jun 2026
· source
· release history
Adds a human-readable Alert Title column to Alerts CSV exports, enabling direct CVE identification without cross-referencing the dashboard.
Alert Titles Added to CSV Exports (2026-06-23) · Jun 2026
· source
· release history
Populates Upgrade Version values more consistently in vulnerability alert CSV exports.
Alert Titles Added to CSV Exports (2026-06-23) · Jun 2026
· source
· release history
Adds an Export as CSV button in the top-right corner of the Organization Alerts page to export alerts respecting applied filters and including an Alert count column.
Export Alerts as CSV · Sep 2025
· source
· release history
+Rust ecosystem scanningshippedDetects security risks and analyzes supply chain dependencies across Rust packages and Cargo workspaces.4 releases · first seen Jul 2025▸
release
Unlocks full SBOM generation for Rust dependencies
Rust Support In Beta · Sep 2025
· source
· release history
Activates Rust-aware supply chain checks in the general beta tier
Rust Support In Beta · Sep 2025
· source
· release history
Enables full Rust project analysis including Cargo workspaces and Cargo.toml-only crates
Rust Support In Beta · Sep 2025
· source
· release history
Provides security scores, maintainer info, and dependency insights for Rust packages
Rust Support Now Available · Jul 2025
· source
· release history
+License compliance managementshippedAllows users to view, customize, and override license detection results on a per-package basis to streamline attribution and compliance reporting.4 releases · first seen Jul 2025▸
release
Enables modifying license detection results on a per-package basis.
New: License Overlays for Custom License Management · Jul 2025
· source
· release history
Introduces the Settings → Legal → License Overlays interface for viewing and managing overlays.
New: License Overlays for Custom License Management · Jul 2025
· source
· release history
Allows editing of license identifiers and author info for cleaner attribution files.
New: License Overlays for Custom License Management · Jul 2025
· source
· release history
Supports applying changes across versions using glob patterns (e.g., 1.*).
New: License Overlays for Custom License Management · Jul 2025
· source
· release history
+Tracked branch configurationshippedLets users add branches by name or glob pattern so that scans, alerts, webhooks, and email notifications are generated across non-default branches such as beta, canary, or legacy.1 release · 2 other sources · first seen Nov 2026▸
Also counts toward: REST API, Web management console, Outbound webhooks (the product notifies you)
release
Add tracked branches using plain names or glob expressions via Settings -> Scans -> Tracked Branches to receive alerts, webhooks, and email notifications across branches such as beta, canary, or legacy.
Organization alerts can now track multiple branches (2026-11-02) · Nov 2026
· source
· release history
example
Track a canary or beta branch alongside main so production ring deployments all surface in org-wide alerts.$ Settings -> Scans -> Tracked Branches -> Add a branch name (e.g. 'canary') or a glob expression (e.g. 'release/*') to begin receiving alerts, webhooks, and emails for that branch.
Organization alerts can now track multiple branches (2026-11-02) · Nov 2026
· source
Register a full scan against a non-default branch via the API so it appears in organization alerts and triggers webhooks.$ curl -X POST https://socket.dev/api/full-scan \ -H 'Authorization: Bearer <token>' \ -H 'Content-Type: application/json' \ -d '{"branch": "canary", "set_as_pending_head": true}'
Organization alerts can now track multiple branches (2026-11-02) · Nov 2026
· source
+Security policy preset updatesshippedRemoves the 'Obfuscated code' alert from the 'Balanced' and 'Comprehensive' security policy presets, requiring explicit configuration to retain those alerts.3 releases · first seen Oct 2026▸
release
Keep Obfuscated code alerts after November 10 by opening Security Policy and setting Obfuscated code to Warn or Monitor instead of Inherit, or by adding a matching rule on the Policies page — the alert will be removed from the Balanced and Comprehensive preset defaults on that date.
changelog · Oct 2026
· source
· release history
The Obfuscated code alert is removed from the Balanced and Comprehensive security policy presets on November 10, 2026; organizations relying on preset defaults will stop receiving this alert unless they explicitly set it to Warn or Monitor.
changelog · Oct 2026
· source
· release history
The Obfuscated code alert is removed from the Balanced and Comprehensive security policy presets on November 10, 2026; organizations relying on preset defaults will no longer receive these alerts unless they explicitly set Obfuscated code to Warn or Monitor via Settings → Security Policy or the Policies…
Obfuscated Code Alert Defaults Changing November 10 (2026-10-27) · Oct 2026
· source
· release history
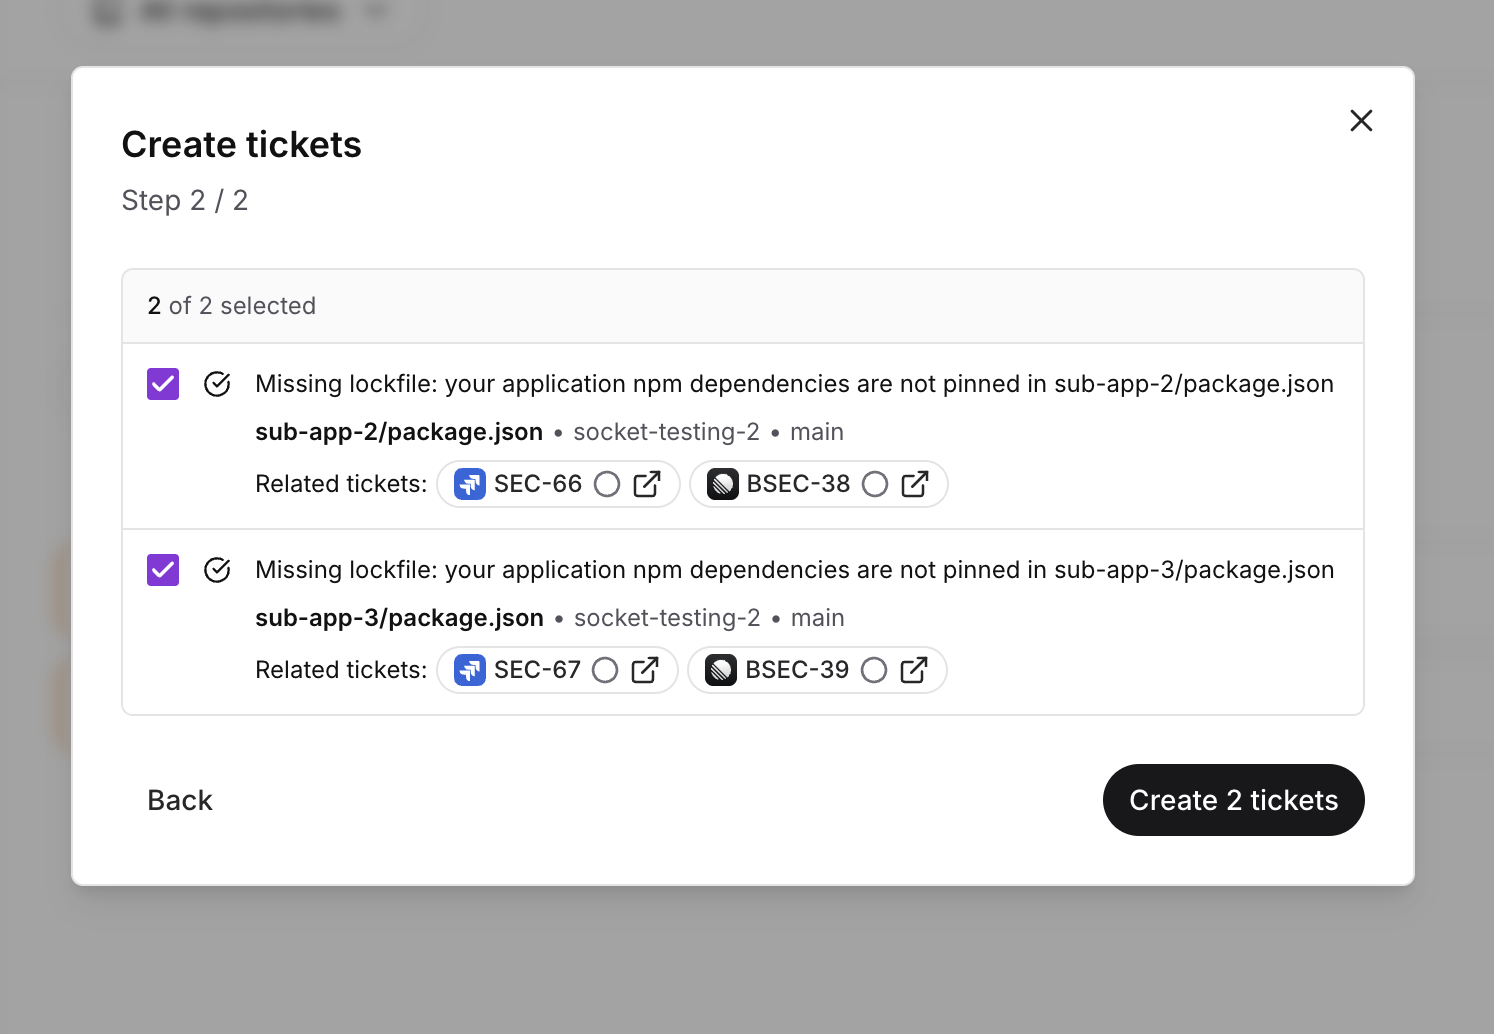
+Bulk issue tracker ticket creationshippedAllows selecting multiple manifest alerts across repositories and creating one ticket per repository and manifest file in Jira, Linear, Asana, or ClickUp in a single action, with support for shift-click range selection.2 releases · 1 other source · first seen Oct 2026▸
Also counts toward: Ticketing integration
release
Bulk-create Jira, Linear, Asana, and ClickUp tickets for manifest alerts (e.g.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Missing lockfile), one ticket per repository and manifest file, scoped to the selected repository and branch.
Faster bulk ticket creation for manifest alerts (2026-10-20) · Oct 2026
· source
· release history
Shift-click to select a range of alerts for bulk actions.
Faster bulk ticket creation for manifest alerts (2026-10-20) · Oct 2026
· source
· release history
example
Select multiple manifest alerts across repositories and create one Jira ticket per repo/manifest in a single action.$ In the Socket dashboard, navigate to your manifest alerts list. Shift-click to select the desired range of alerts, then choose 'Create tickets' and select Jira (or Linear, Asana, or ClickUp) to…
Faster bulk ticket creation for manifest alerts (2026-10-20) · Oct 2026
· source
+Package tag and commit history inspectionshippedDisplays the full commit history for force-pushed tags on package pages, allowing review of commits a version previously referenced before a tag was overwritten.3 releases · first seen Jul 2026▸
release
Displays full commit history for force-pushed tags on Packagist package pages, with the currently associated commit highlighted.
Packagist Package Pages Now Surface Force-Pushed Tags (2026-07-06) · Jul 2026
· source
· release history
Packagist package pages now display the full commit history for force-pushed tags, with the current tag commit highlighted
Packagist Package Pages Now Surface Force-Pushed Tags (2026-07-06) · Jul 2026
· source
· release history
Enables review of commits a package version previously referenced before a tag was overwritten.
Packagist Package Pages Now Surface Force-Pushed Tags (2026-07-06) · Jul 2026
· source
· release history
+Manifest scan enhancementsshippedImproves detection and remediation for missing lockfiles by identifying manifest alerts, providing impact details, and allowing direct ticket creation.3 releases · first seen Jun 2026▸
Also counts toward: Ticketing integration
release
Adds Manifest Alerts view to scan results for detecting missing lockfiles in application and project repositories
New: Manifest Alerts for missing lockfiles · Jun 2026
· source
· release history
Adds controls to ignore/restore Manifest Alerts and create Jira or Linear tickets directly from the alert
New: Manifest Alerts for missing lockfiles · Jun 2026
· source
· release history
Supports impact details and remediation for npm, pnpm, yarn, and bun ecosystems when a manifest lacks a corresponding lockfile
New: Manifest Alerts for missing lockfiles · Jun 2026
· source
· release history
+Session management controlsshippedProvides users with the ability to view and terminate active account sessions for improved account security.3 releases · first seen Oct 2025▸
release
Adds a new Security tab in the User Preferences UI to view and terminate active account sessions
Add Security settings for active sessions · Apr 2026
· source
· release history
Enables secret and container scanning configuration via expanded config keys
Expanded: Socket Basics Configuration · Oct 2025
· source
· release history
Supports per-language rule customization across 17 language SAST scanners
Expanded: Socket Basics Configuration · Oct 2025
· source
· release history
+AI-assisted development integrationshippedProvides real-time dependency scoring and threat data to AI assistants and LLM tools via MCP server.3 releases · first seen May 2025▸
Also counts toward: MCP server
release
Adds the option to use the Socket MCP server via the hosted service at https://mcp.socket.dev instead of running it locally.
Socket MCP Now Available as a Hosted Service · Jun 2025
· source
· release history
Launches socket-mcp, an experimental MCP server that brings real-time dependency scoring to AI-assisted development
Socket MCP: Real-Time Dependency Scoring for AI Tools · May 2025
· source
· release history
Enables tools such as GitHub Copilot, Claude, and other LLM integrations to query Socket’s depscore API directly during code generation
Socket MCP: Real-Time Dependency Scoring for AI Tools · May 2025
· source
· release history
+Socket Firewall extension supportshippedExtends firewall capabilities to block or filter malicious Chrome and VS Code extensions at the network or marketplace level.2 releases · first seen Jun 2026▸
release
Enables blocking at extension asset and VSIX download URLs in the Socket Firewall closed beta.
New: Socket Firewall support for VS Code and Open VSX · Jun 2026
· source
· release history
Adds Socket Firewall support for VS Code and Open VSX to filter flagged extensions from marketplace results.
New: Socket Firewall support for VS Code and Open VSX · Jun 2026
· source
· release history
+VS Code extension scanningshippedScans OpenVSX extensions for security risks and displays compatibility metadata.2 releases · first seen May 2026▸
release
Homepage links are shown for OpenVSX extensions when available
Add OpenVSX categories, compatibility, and homepage metadata · May 2026
· source
· release history
VS Code version compatibility information is displayed for OpenVSX extensions
Add OpenVSX categories, compatibility, and homepage metadata · May 2026
· source
· release history
+GitHub sync managementshippedAllows users to control GitHub organization integration synchronization via the dashboard interface, including selective syncing of installations.2 releases · first seen Mar 2026▸
Also counts toward: Web management console
release
Adds UI option to sync a single GitHub installation via Dashboard → Integrations → GitHub
Sync Individual GitHub Installations · Mar 2026
· source
· release history
Clarifies that the Sync all GitHub installations button syncs every linked organization installation
Sync Individual GitHub Installations · Mar 2026
· source
· release history
+PURL-based redirection and scanningshippedEnables universal package lookup via PURLs and supports organization-specific policy application for unified package resolution.2 releases · first seen Jan 2026▸
Also counts toward: REST API
release
Adds a new standardized PURL-based redirect endpoint at /purl/$URL_ENCODED_PURL that routes to the correct package page regardless of ecosystem
Universal PURL Redirect for Package Pages · Feb 2026
· source
· release history
Adds POST /v0/orgs/{org_slug}/purl endpoint to apply organization-specific policies based on repository labels
New: Organization-Scoped PURL Endpoint · Jan 2026
· source
· release history
+Socket Firewall Enterprise deploymentshippedOffers flexible deployment options for Socket Firewall, including long-lived HTTPS proxy support for on-prem environments.2 releases · first seen Oct 2025▸
Also counts toward: Self-hosted deployment
release
Adds Socket Firewall Enterprise edition with flexible deployment options including long-lived HTTPS proxy for on-prem environments
New: Socket Firewall Enterprise · Oct 2025
· source
· release history
Introduces MUSL build for improved compatibility with CI pipelines and containerized deployments
New: Socket Firewall Enterprise · Oct 2025
· source
· release history
+GitHub Actions workflow scanningshippedDetects security and license risks in GitHub Actions workflows through deep package inspection.2 releases · first seen Oct 2025▸
release
Supports scanning GitHub Actions workflows for security and license risks via deep package inspection
New: GitHub Actions Scanning Support · Oct 2025
· source
· release history
Detects malicious or obfuscated code in action dependencies using the Argus taint-tracking engine
New: GitHub Actions Scanning Support · Oct 2025
· source
· release history
+API key managementshippedIssues and displays API keys in a consistent masked format for use in integrations.1 release · first seen Oct 2026▸
release
API keys now use a new consistent masked format (e.g. sktsec_…Xy9Q); integrations that parse the previous masked format may need updating.
changelog · Oct 2026
· source
· release history
+Pull request scanning and commentingshippedPosts automated dependency overviews, scores, and severity labels to pull requests, updating dynamically as changes occur.1 release · first seen Oct 2026▸
release
Posts PR comments with dependency overviews, scores, severity labels, and report links, updating automatically as the PR changes.
announced · Oct 2026
· source
· release history
+Extended GitHub repository metadatashippedSurfaces additional repository context such as stargazer count, open issues, and archival status on package pages to aid risk assessment.1 release · first seen Jan 2026▸
release
Surface related GitHub metadata including repository avatar, open issues, pull requests, archived or disabled status, and stargazer reputation
Update Swift repository metadata · Jan 2026
· source
· release history
+Supply chain protection for AI modelsshippedProvides experimental scanning to detect hidden payloads in AI model frameworks and supports integration via API or AIBOM.1 release · first seen Oct 2025▸
release
Socket introduces experimental supply chain protection for AI models, allowing users to detect hidden payloads in major frameworks and integrate scanning via API or AIBOM.
Experimental Malware Scanning for Hugging Face Models · Oct 2025
· source
· release history
+Custom organizational tabsshippedAllows users to create, rename, duplicate, and delete custom tabs on the organization alerts page for business and enterprise plans.1 release · first seen Oct 2025▸
release
Adds the ability to create, rename, duplicate, and delete custom tabs on the org alerts page for business and enterprise plans.
New: Custom Tabs in Org Alerts · Oct 2025
· source
· release history
+Chrome extension scanningshippedDetects malware, risky permissions, and silent supply chain attacks in Chrome extensions.1 release · first seen Jul 2025▸
release
Expands Socket's scope to scan Chrome extensions for malware, risky permissions, and silent supply chain attacks
Experimental Protection for Chrome Extensions · Jul 2025
· source
· release history
+.NET dependency graph analysisshippedPerforms deep analysis of .NET dependency graphs, including transitive and conditionally imported packages.1 release · first seen Apr 2025▸
release
Enables deep analysis of .NET dependency graphs including transitive and conditionally imported packages
.NET Support Now in Public Beta · Apr 2025
· source
· release history
+Go ecosystem scanningshippedDetects obfuscation, backdoors, and exec.Command misuse in Go projects via go.mod and go.sum files.1 release · first seen Apr 2025▸
release
Adds Go ecosystem support to socket scanning, detecting obfuscation, backdoors, and exec.Command misuse in projects with go.mod and go.sum files
Go Support Now Generally Available · Apr 2025
· source
· release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
21 commands for Socket, each
with where it came from. This tool has no source analysis yet, so there
is no option reference and no captured run beside them.
View
Source
No command matches.
Screenshots
From the release notes, newest first. Click one to see it full size.
Breaking-change disciplinehow rarely a release breaks users, and notice given
Maintenance riskquiet time against its own cadence, maintainers
Innovation & surfacenew capabilities, API and MCP surface
Five scores for Socket, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Each score is 0–100 on a published rubric, derived from data this site already shows.
A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
Documentation quality — the release-notes rubric published on the analytics page, unchanged.
Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Socket puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
38 readings of Socket's pricing page since Sep 2022, with 3 relaunches of its plan lineup and 12 changes to what its plans include — each one dated, compared with the reading before it, and explained for someone buying the tool.
Pricing and packaging history is included with Researcher and Business. See how every vendor we track sells, and how that has changed over time, using data we don't publish anywhere else.
Each offering on the pricing page links to its own page of plans, read at its latest capture.
Plan relaunches
Plans, prices and descriptions are quoted from the vendor's own pricing page as we read it on each date.
A plan missing from a later reading is shown as no longer listed on the page — a statement about the page, not the product.
Readings that failed to show any plans are left out rather than read as a change.
Website history
socket.dev, every change
Socket's home page and 25 more pages as they looked each month from August 2021 to October 2026: 34 renders, 4 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
What Socket connects to, runs on and detects, read from its release notes and docs. So far: 7 updated supported platforms, 1 updated detection, 1 new supported platform.
Show
9 changes, tracked since Oct 6, 2026.
Oct 272026
updatedObfuscated code alert removed from 'Balanced' and 'Comprehensive' preset defaults
On November 10, 2026, we're removing the Obfuscated code alert from our "Balanced" and "Comprehensive" security policy presets ("Essential" doesn't include it and won't change).
Obfuscated Code Alert Defaults Changing November 10 (2026-10-27)Source ↗
Oct 102026
updatedPython reachability analysis soundness, memory usage and PyTorch modeling improvements
Soundness and memory usage improvements for the Python reachability analysis. More precise modeling of PyTorch prevents analysis blow-ups in projects that use it.
updatedSocket Fix Python upgrades overhauled to follow each tool's own resolution, including uv, pip-compile, uv pip compile
With Poetry, Pipenv
upgrades for Python are overhauled to follow each tool's own resolution: uv, pip-compile and uv pip compile locks are regenerated with the tool itself. Poetry and Pipenv projects are now supported.
Nothing first seen in this window. That doesn't mean Socket shipped nothing, only that we found no record of it.
Changes per month New Updated Retired
2026-10
9
How we count
Read from 8 of 304 release notes and docs updates we hold for Socket. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through Socket's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
Show
Coverage in all entries
304 entries
No entries match these filters.
November 20261
October 202612
September 202619
August 202615
July 20263
June 202618
May 20267
April 20264
March 20266
February 20267
January 202615
December 202510
November 202520
October 202513
September 202519
August 202513
July 202518
June 202513
May 20255
April 202518
March 20253
February 202513
January 20255
December 20245
November 20249
October 20245
September 20246
August 20246
July 20249
June 20247
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can
follow every release here.
 Organization alerts can now track multiple branches (2026-11-02) · Nov 2026
· source
· release history
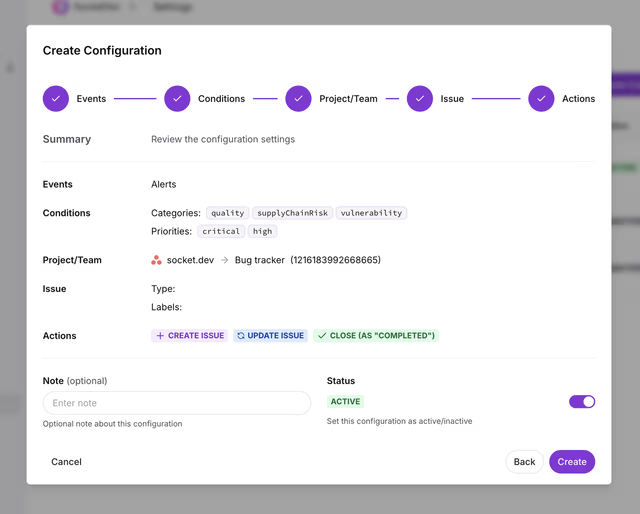 New: Asana integration for alert ticketing (2026-08-25) · Aug 2026
· source
· release history
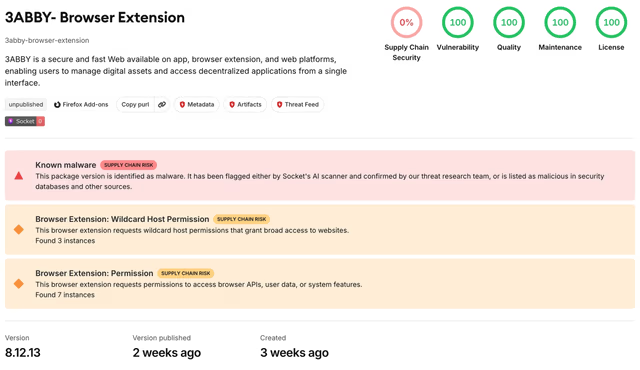 New: Firefox extension protection (2026-08-20) · Aug 2026
· source
· release history
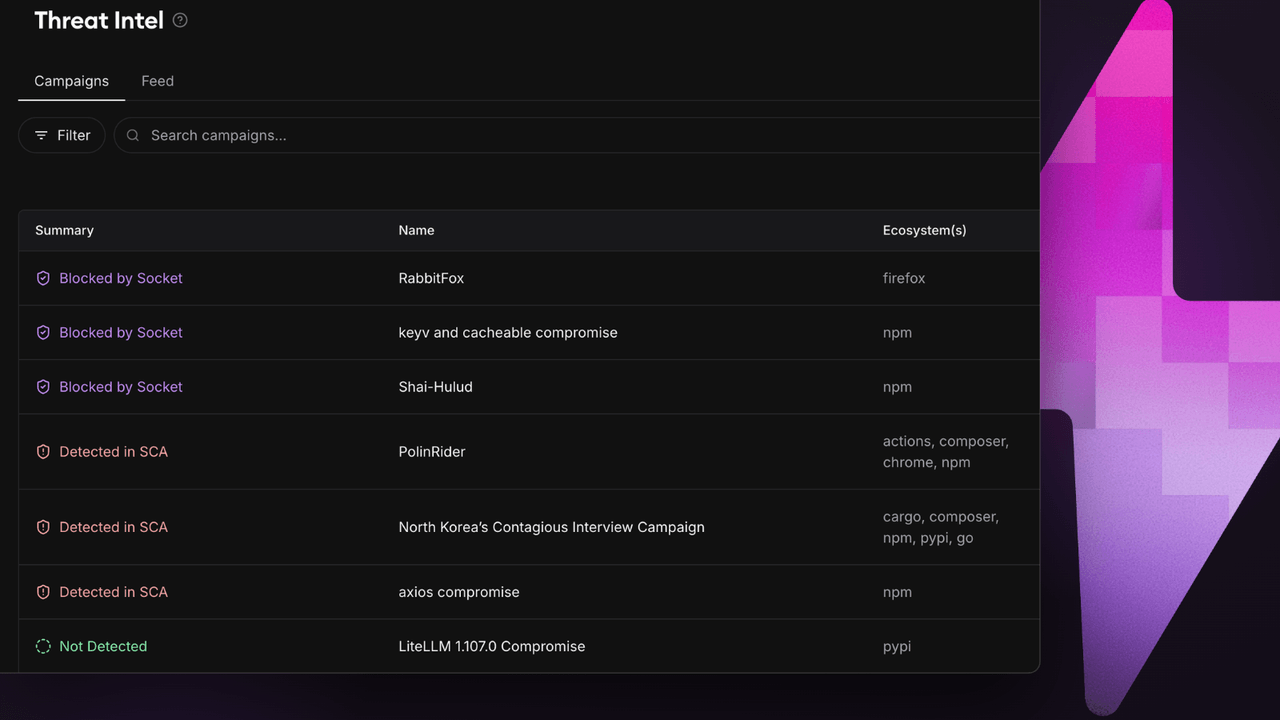 announced · Oct 2026
· source
· release history
 Faster bulk ticket creation for manifest alerts (2026-10-20) · Oct 2026
· source
· release history
 Choose a badge style and copy the code →