No entries match these filters. Clear filters
Bots - Granular access controls for the top Personal Agents (2026-11-04)
Nov 4, 2026
·
issue 129
Cloudflare adds per-agent access controls for top Personal Agents under AI Crawler and Agent access policies︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
Allow specific Personal Agents to access your site while your broader agent policy is more restrictive.
📍 In the Cloudflare dashboard, go to Security › Settings › AI Crawler and Agent access policies, locate the Personal Agents section, and set the action for each listed Personal Agent individually (e.g., Allow for a specific agent while keeping others blocked).
Set per-agent access actions for individual top Personal Agents via Security > Settings > AI Crawler and Agent access policies , replacing the former Configure AI bot policies setting.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Personal Agents now inherit the existing Agents policy by default, with Cloudflare recommending Allow (do not block) as the default action.
Set per-agent access actions for individual top Personal Agents via Security > Settings > AI Crawler and Agent access policies , replacing the former Configure AI bot policies setting.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
1 more in Everything
WAF - WAF Release - 2026-11-03 (2026-11-03)
Nov 3, 2026
·
issue 130
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
WAF - WAF Release - Scheduled changes for 2026-11-10 (2026-11-03)
Nov 3, 2026
·
issue 130
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Cloudflare adds a SCIM SCIM A standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave. Keyless SSL Keyless SSL A TLS termination architecture where the private key never leaves the key owner's server; a remote process handles only the cryptographic operations that require it, letting a CDN or proxy terminate connections without holding the key.
Inspect provisioned users and groups in Cloudflare One with a new SCIM population viewer that lets you search SCIM users and groups, inspect resource attributes, and investigate provisioning issues.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Analyze account activity over time and investigate actions, actors, products, and failures with Audit Logs v2 account analytics. Route Cloudflare WAN traffic through a selected Gateway processing region for TLS decryption and HTTP inspection. Keyless SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination. ECDSA ECDSA The elliptic-curve signature algorithm behind most TLS certificates, blockchains and many hardware keys. It is one of the algorithms post-quantum signatures are meant to replace. Active Durable Objects now defer code updates by default, allowing up to 5 minutes to finish work before adopting new code; the delay is configurable or can be bypassed for immediate updates.
+1 more
show less
Browser Run now uses Chrome 152 as its default browser.
Inspect provisioned users and groups in Cloudflare One with a new SCIM population viewer that lets you search SCIM users and groups, inspect resource attributes, and investigate provisioning issues.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Analyze account activity over time and investigate actions, actors, products, and failures with Audit Logs v2 account analytics. Route Cloudflare WAN traffic through a selected Gateway processing region for TLS decryption and HTTP inspection.
3 more in Everything
└──▷ BREAKING ON UPGRADE
! Beginning November 4, 2026, D1 queries that return a result larger than 50 MB will fail and return an error.! The classic DNS records page has been retired; all users now use the new DNS records experience.
Workers, BYOIP, Bots - Workers subrequests now preserve context for BYOIP destinations (2026-10-30)
Oct 30, 2026
·
issue 126
Cloudflare Workers now preserves subrequest context for BYOIP BYOIP Bring Your Own IP — a cloud provider feature letting customers move their own publicly routable IP blocks into the provider's network, so traffic to those addresses routes through the cloud without renumbering.
Workers subrequests to BYOIP-proxied hostnames now preserve the CF-Worker header and cf.worker.upstream_zone field, enabling consistent security rule evaluation across same-zone and cross-zone subrequests.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Bot Management fields on BYOIP destination zones now reflect the original end-user connection rather than the internal Cloudflare service connection, so bot scores, verified bot status, and JA3 JA3 A method for fingerprinting TLS clients by hashing fields from the ClientHello message, producing a short string that identifies the TLS library or application making a connection regardless of IP or port. JA4 JA4 A network fingerprinting method that hashes observable TLS handshake fields into a short, readable tag, giving cyber tools a stable, version-agnostic way to classify clients and detect anomalies. Cross-zone Workers subrequests to BYOIP destinations now set CF-Connecting-IP to the Workers client IP address 2a06:98c0:3600::103; same-zone subrequests continue to reflect the original client IP through CF-Connecting-IP .
Workers subrequests to BYOIP-proxied hostnames now preserve the CF-Worker header and cf.worker.upstream_zone field, enabling consistent security rule evaluation across same-zone and cross-zone subrequests.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
2 more in Everything
└──▷ BREAKING ON UPGRADE
! Cross-zone Workers subrequests to Cloudflare-proxied BYOIP hostnames now set CF-Connecting-IP to 2a06:98c0:3600::103 instead of the original client IP. Any security rule or application logic on the destination zone that reads CF-Connecting-IP to allow/block specific IPs for cross-zone subrequest traffic must be updated.
Cloudflare adds MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
└──▷ USE IT
Lock a Workflow to a specific jurisdiction so its instances only run and store data in that region.
wrangler.toml
copy
# wrangler.toml
[[workflows]]
name = "my-workflow"
binding = "MY_WORKFLOW"
class_name = "MyWorkflow"
jurisdiction = "eu"
Discover which attributes keys are available in an Analytics dataset without the deprecated include_custom_attributes flag.
copy
$ curl 'https://api.cloudflare.com/client/v4/accounts/<account_id>/analytics_engine/sql/introspect?dataset=<dataset>&include_attributes=true' \
-H 'Authorization: Bearer <token>'
Serve Workers Static Assets from a URL path prefix by setting the prefix in Wrangler or cloudflare.config.ts.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Restrict where a Workflow's instances run and store data by setting a jurisdiction in your Wrangler configuration. Filter MCP tool-call analytics by response status — counting successful, failed, or cached calls separately, with successful calls as the default view. Discover attributes keys in the SQL API introspection endpoint using the new include_attributes parameter. Preview an Agents SDK dev server through internal hostnames in the browser without public URLs or a prebuilt harness adapter.
+2 more
show less
Create custom login, denial, and command-line approval pages for Cloudflare Access with request-specific content. Workers Builds now retains each build and its build logs for 90 days.
Serve Workers Static Assets from a URL path prefix by setting the prefix in Wrangler or cloudflare.config.ts.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Restrict where a Workflow's instances run and store data by setting a jurisdiction in your Wrangler configuration. Filter MCP tool-call analytics by response status — counting successful, failed, or cached calls separately, with successful calls as the default view. Preview an Agents SDK dev server through internal hostnames in the browser without public URLs or a prebuilt harness adapter. Create custom login, denial, and command-line approval pages for Cloudflare Access with request-specific content.
2 more in Everything
└──▷ BREAKING ON UPGRADE
! The include_custom_attributes parameter on the SQL API introspection endpoint is deprecated in favour of include_attributes.
API surface changed: +12 endpoints, 55 modified︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
API change API surface changed: +12 endpoints, 55 modified︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
+ DELETE /accounts/{account_id}/cloudforce-one/events/dataset/{dataset_id}/indicators + DELETE /accounts/{account_id}/firewall/payload_logging/key + DELETE /accounts/{account_id}/realtime/kit/{app_id}/meetings/{meeting_id}/participants/{participant_id}/token + DELETE /zones/{zone_id}/firewall/payload_logging/key + GET /accounts/{account_id}/access/organizations/trust_settings + GET /accounts/{account_id}/firewall/payload_logging/key + GET /zones/{zone_id}/firewall/payload_logging/key + PATCH /accounts/{account_id}/access/organizations/trust_settings + PATCH /accounts/{account_id}/dns_settings/nameserver_sets/{nameserver_set_id} + PUT /accounts/{account_id}/access/organizations/trust_settings + PUT /accounts/{account_id}/firewall/payload_logging/key + PUT /zones/{zone_id}/firewall/payload_logging/key
~ DELETE /accounts/{account_id}/ai-gateway/gateways/{id}: response schema changed ~ GET /accounts/{account_id}/abuse-reports/{report_id}/appeals/eligibility: response schema changed ~ GET /accounts/{account_id}/ai-gateway/gateways: response schema changed ~ GET /accounts/{account_id}/ai-gateway/gateways/{id}: response schema changed ~ GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles: response schema changed ~ GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/relevance/aggregate: param read (query) added ~ GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/severity/aggregate: param pir_id (query) added; param read (query) added; response schema changed ~ GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}: response schema changed ~ GET /accounts/{account_id}/devices/physical-devices: response schema changed ~ GET /accounts/{account_id}/devices/physical-devices/{device_id}: response schema changed ~ GET /accounts/{account_id}/one/integrations: response schema changed ~ GET /accounts/{account_id}/reporting/industry: response schema changed ~ GET /accounts/{account_id}/reporting/policies: response schema changed ~ GET /accounts/{account_id}/reporting/policies/{policy_id}: response schema changed ~ GET /accounts/{account_id}/reporting/reports: response schema changed ~ GET /accounts/{account_id}/reporting/reports/{report_id}: response schema changed ~ GET /accounts/{account_id}/urlscanner/v2/result/{scan_id}: response schema changed ~ GET /accounts/{account_id}/workflows: response schema changed ~ GET /accounts/{account_id}/workflows/{workflow_name}: response schema changed ~ GET /radar/annotations: response schema changed ~ GET /radar/annotations/outages: response schema changed ~ GET /radar/annotations/{id}: response schema changed ~ GET /radar/traffic_anomalies: response schema changed ~ GET /radar/traffic_anomalies/{uuid}: response schema changed ~ GET /zones/{zone_id}/bot_management: response schema changed ~ GET /zones/{zone_id}/fraud_detection/settings: response schema changed ~ PATCH /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}: response schema changed ~ PATCH /accounts/{account_id}/devices/physical-devices/{device_id}: response schema changed ~ PATCH /accounts/{account_id}/devices/policy: request body changed ~ PATCH /accounts/{account_id}/devices/policy/{policy_id}: request body changed ~ PATCH /accounts/{account_id}/reporting/industry: response schema changed ~ POST /accounts/{account_id}/abuse-reports/{report_id}/mitigations/appeal: request body changed ~ POST /accounts/{account_id}/basin-catalog/{bucket_name}/enable: request body changed ~ POST /accounts/{account_id}/bulk/subscriptions: request body changed ~ POST /accounts/{account_id}/devices/policy: request body changed ~ POST /accounts/{account_id}/dns_settings/nameserver_sets: request body changed ~ POST /accounts/{account_id}/logpush/jobs: request body changed ~ POST /accounts/{account_id}/r2-catalog/{bucket_name}/enable: request body changed ~ POST /accounts/{account_id}/realtime/kit/{app_id}/meetings/{meeting_id}/participants: response schema changed ~ POST /accounts/{account_id}/realtime/kit/{app_id}/meetings/{meeting_id}/participants/{participant_id}/token: response schema changed ~ POST /accounts/{account_id}/subscriptions: request body changed ~ POST /accounts/{account_id}/subscriptions/{subscription_identifier}/action/append: request body changed ~ POST /accounts/{account_id}/urlscanner/scan: request body changed ~ POST /accounts/{account_id}/urlscanner/v2/scan: request body changed ~ POST /user/subscriptions: request body changed ~ POST /zones/{zone_id}/logpush/jobs: request body changed ~ POST /zones/{zone_id}/subscription: request body changed ~ POST /zones/{zone_id}/subscriptions: request body changed ~ PUT /accounts/{account_id}/subscriptions/{subscription_identifier}: request body changed ~ PUT /accounts/{account_id}/workflows/{workflow_name}: request body changed; response schema changed ~ PUT /user/subscriptions/{identifier}: request body changed ~ PUT /zones/{zone_id}/bot_management: response schema changed ~ PUT /zones/{zone_id}/fraud_detection/settings: response schema changed ~ PUT /zones/{zone_id}/subscription: request body changed ~ PUT /zones/{zone_id}/subscriptions: request body changed
New endpoint DELETE /accounts/{account_id}/cloudforce-one/events/dataset/{dataset_id}/indicators︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New endpoint DELETE /accounts/{account_id}/firewall/payload_logging/key New endpoint DELETE /accounts/{account_id}/realtime/kit/{app_id}/meetings/{meeting_id}/participants/{participant_id}/token New endpoint DELETE /zones/{zone_id}/firewall/payload_logging/key New endpoint GET /accounts/{account_id}/access/organizations/trust_settings
+5 more
show less
New endpoint GET /accounts/{account_id}/firewall/payload_logging/key New endpoint GET /zones/{zone_id}/firewall/payload_logging/key New endpoint PATCH /accounts/{account_id}/access/organizations/trust_settings New endpoint PATCH /accounts/{account_id}/dns_settings/nameserver_sets/{nameserver_set_id} New endpoint PUT /accounts/{account_id}/access/organizations/trust_settings
10 details in Everything
Cloudflare adds HTML/Liquid Access page templates, Workflow jurisdictions, three new OpenTelemetry OpenTelemetry An open standard and set of tools for collecting traces, metrics and logs from applications. It lets services export observability data without tying instrumentation to one monitoring vendor. include_attributes.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Discover all attribute keys available in your HTTP requests dataset for use in SQL queries like attributes['http.method'].
copy
$ curl --get 'https://api.cloudflare.com/client/v4/analytics/sql/introspection' -H 'Authorization: Bearer <API_TOKEN>' --data-urlencode 'account_tag=<ACCOUNT_TAG>' --data-urlencode 'dataset_name=events.httpRequests' --data-urlencode 'include_attributes=true' Pin a Workflow to EU data centers to satisfy GDPR GDPR EU regulation enacted in 2018 that governs how organizations collect, store, and process personal data of EU residents, giving cyber tools legal obligations around data handling and breach notification.
wrangler.toml
copy
[[workflows]]
name = "my-workflow"
binding = "MY_WORKFLOW"
class_name = "MyWorkflow"
jurisdiction = "eu"
Return the active trace ID in an error response so clients and logs can be correlated to the same Workers trace.
javascript
copy
import { tracing } from 'cloudflare:workers';
export default async (request, env) => {
const root = tracing.getActiveSpan();
return tracing.startActiveSpan('handle', async (span) => {
try {
const response = await routeHandler(request, env);
span.setStatus({ code: 'ok' });
return response;
} catch (err) {
span.recordException(err);
span.setStatus({ code: 'error', message: 'Route handler failed' });
return Response.json(
{ error: 'Internal error', traceId: root?.spanContext().traceId },
{ status: 500 }
);
} finally {
span.end();
}
});
};
Adds include_attributes query parameter to the SQL API introspection endpoint (GET https://api.cloudflare.com/client/v4/analytics/sql/introspection), returning discovered attribute keys and their types from the preceding seven days of data in an attributes response field.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds jurisdiction field to workflows bindings in wrangler.toml / wrangler JSON config, supporting values eu, us, and fedramp, so Workflow instances only run and store data within that jurisdiction (requires Wrangler 4.152.0 or above). Adds span.spanContext() , span.setStatus(status) , and span.updateName(name) methods to custom spans in Workers, aligning with the OpenTelemetry span API and enabling trace/span ID correlation, status export, and dynamic span renaming. Adds onInterrupt: 'replay' option to WorkerJavaScriptBackend in @cloudflare/computer (v0.7.0+), allowing agent workspaces to resume interrupted runs after a deploy or crash by replaying recorded call results. Adds ctx.interrupt() support inside custom modules on WorkerJavaScriptBackend, enabling a function to pause a run until an external approval decision is supplied via workspace.runtime.respond() .
+3 more
show less
Adds workspace.runtime.pending() and workspace.runtime.respond() APIs to @cloudflare/computer for fetching and resolving pending approval calls in agent workspaces. Adds nameservers.type: 'cloudflare.advanced' value to DNS settings endpoints (/zones/{zone_id}/dns_settings and /accounts/{account_id}/dns_settings) to represent Advanced Nameservers, replacing the previous foundation_dns: true boolean. Supports fully custom HTML and Liquid templates for Cloudflare Access user-facing pages (login, identity-denied, forbidden, and command-line approval), assignable per application or as account defaults from the Cloudflare One dashboard.
Adds include_attributes query parameter to the SQL API introspection endpoint (GET https://api.cloudflare.com/client/v4/analytics/sql/introspection), returning discovered attribute keys and their types from the preceding seven days of data in an attributes response field.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds jurisdiction field to workflows bindings in wrangler.toml / wrangler JSON config, supporting values eu, us, and fedramp, so Workflow instances only run and store data within that jurisdiction (requires Wrangler 4.152.0 or above). Adds onInterrupt: 'replay' option to WorkerJavaScriptBackend in @cloudflare/computer (v0.7.0+), allowing agent workspaces to resume interrupted runs after a deploy or crash by replaying recorded call results. Adds ctx.interrupt() support inside custom modules on WorkerJavaScriptBackend, enabling a function to pause a run until an external approval decision is supplied via workspace.runtime.respond() . Adds workspace.runtime.pending() and workspace.runtime.respond() APIs to @cloudflare/computer for fetching and resolving pending approval calls in agent workspaces.
+1 more
show less
Supports fully custom HTML and Liquid templates for Cloudflare Access user-facing pages (login, identity-denied, forbidden, and command-line approval), assignable per application or as account defaults from the Cloudflare One dashboard.
2 more in Everything
└──▷ BREAKING ON UPGRADE
! A Workflow's jurisdiction is set at creation time and cannot be changed afterwards; if an existing Workflow has a different jurisdiction, wrangler deploy and wrangler versions upload will stop before uploading.! DNS settings endpoints will stop accepting the foundation_dns boolean in a future API change; clients must migrate writes to nameservers.type: 'cloudflare.advanced'. Currently, requests that include both nameservers.type and foundation_dns with conflicting values are rejected.! Clients that treat nameservers.type as a closed enum must be updated to recognize the new 'cloudflare.advanced' value or they will break when the seven-day rollout reaches their account.
China Network, Challenges, Bots - China-native Challenge Pages for the China Network (2026-10-28)
Oct 28, 2026
·
issue 124
Cloudflare China Network now serves Turnstile challenge widgets hosted inside Mainland China, eliminating cross-border requests for visitors there︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Cloudflare adds an interactive Radar homepage, npm version pinning via packageManager in Workers Builds, and tightens D1 undelete to 7 days.
Redesigned Cloudflare Radar homepage with an interactive traffic and outages map, curated insights section with tabbed navigation, and updated Kumo-based interface. Workers Builds now pins the npm version from the packageManager field in package.json, ensuring build and local environments use the same npm version.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! The D1 undelete API now only restores databases deleted within the last 7 days; databases deleted earlier than that can no longer be recovered via the API.
WAF - WAF Release - 2026-10-25 - Emergency - Cloudflare Managed Ruleset (2026-10-25)
Oct 25, 2026
·
issue 120
└──▷ BREAKING ON UPGRADE
! If you have a ruleset-level action override that applies Block, the new Brotli (...ca706f3c) and Next.js image optimizer (...402fe5bb) rules may begin blocking legitimate traffic immediately on deployment, despite their default Log action — review existing ruleset overrides before upgrading.
API surface changed: +21 endpoints, −2 endpoints, 140 modified︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
New endpoint DELETE /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/profile︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New endpoint DELETE /accounts/{account_id}/email/domains/{email_domain_id} New endpoint DELETE /zones/{zone_id}/settings/aegis New endpoint GET /_heartbeat New endpoint GET /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/matches/aggregate
+5 more
show less
New endpoint GET /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/profile New endpoint GET /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/{priority_id}/matches/aggregate New endpoint GET /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/{priority_id}/matches/series New endpoint GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/relevance/aggregate New endpoint GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/severity/aggregate
10 details in Everything
└──▷ BREAKING ON UPGRADE
! Removed endpoint GET /api/v4/health! Removed endpoint POST /accounts/{account_id}/pay-bad-debt! DELETE /accounts/{account_id}/brand-protection/brands: response schema changed! DELETE /accounts/{account_id}/brand-protection/brands/patterns: response schema changed! DELETE /accounts/{account_id}/brand-protection/logos/{logo_id}: response schema changed! DELETE /accounts/{account_id}/brand-protection/queries: response schema changed! GET /accounts/{account_id}/brand-protection/alerts: response schema changed! GET /accounts/{account_id}/brand-protection/brands: response schema changed! GET /accounts/{account_id}/brand-protection/brands/patterns: response schema changed! GET /accounts/{account_id}/brand-protection/domain-info: response schema changed! GET /accounts/{account_id}/brand-protection/logo-matches: response schema changed! GET /accounts/{account_id}/brand-protection/logo-matches/download: response schema changed! GET /accounts/{account_id}/brand-protection/logos: response schema changed! GET /accounts/{account_id}/brand-protection/logos/{logo_id}: response schema changed! GET /accounts/{account_id}/brand-protection/matches: response schema changed! GET /accounts/{account_id}/brand-protection/matches/download: response schema changed! GET /accounts/{account_id}/brand-protection/queries: response schema changed! GET /accounts/{account_id}/brand-protection/recent-submissions: response schema changed! GET /accounts/{account_id}/brand-protection/submission-info: response schema changed! GET /accounts/{account_id}/brand-protection/total-queries: response schema changed! GET /accounts/{account_id}/brand-protection/tracked-domains: response schema changed! GET /accounts/{account_id}/brand-protection/url-info: response schema changed! GET /live: response schema changed! GET /ready: response schema changed! GET /signed-url: response schema changed! PATCH /accounts/{account_id}/brand-protection/alerts: response schema changed! PATCH /accounts/{account_id}/brand-protection/alerts/clear: response schema changed! PATCH /accounts/{account_id}/brand-protection/alerts/refute: response schema changed! PATCH /accounts/{account_id}/brand-protection/alerts/verify: response schema changed! PATCH /accounts/{account_id}/brand-protection/clear: response schema changed! PATCH /accounts/{account_id}/brand-protection/queries: response schema changed! PATCH /accounts/{account_id}/brand-protection/refute: response schema changed! PATCH /accounts/{account_id}/brand-protection/verify: response schema changed! POST /accounts/{account_id}/brand-protection/brands: response schema changed! POST /accounts/{account_id}/brand-protection/brands/patterns: response schema changed! POST /accounts/{account_id}/brand-protection/logos: response schema changed! POST /accounts/{account_id}/brand-protection/queries: request body changed; response schema changed! POST /accounts/{account_id}/brand-protection/queries/bulk: response schema changed! POST /accounts/{account_id}/brand-protection/queries/{query_id}/matches/{domain_id}/dismiss: response schema changed! POST /accounts/{account_id}/brand-protection/queries/{query_id}/matches/{domain_id}/undismiss: response schema changed! POST /accounts/{account_id}/brand-protection/scan-logo: response schema changed! POST /accounts/{account_id}/brand-protection/scan-page: response schema changed! POST /accounts/{account_id}/brand-protection/search: response schema changed! POST /accounts/{account_id}/brand-protection/submit: response schema changed! POST /internal/submit: response schema changed
Cloudflare Tunnel gains URL normalization in cloudflared 2026.10.0; a new Tunnel Read And Monitor role goes GA; Flagship adds structured evaluation context; MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. /sse.
Updated detection Cloudflare Tunnel supports URL normalization starting with cloudflared 2026.10.0; new releases will enable it by default from 2027-01-25.Adds a new Tunnel Read And Monitor role (generally available) that delegates read access and log streaming for specific Cloudflare Tunnels without granting write access or account-wide permissions. Adds structured evaluation context to Flagship feature flags, supporting nested objects, arrays, and null values with dot-path targeting and array membership operators. Cloudflare MCP servers now serve only /mcp — the /sse endpoint is retired. Agents SDK v0.30.0 supports Pi 1.4, enables Durable Object hibernation while Pi tasks sleep, and improves recovery from crash loops and storage errors.
5 details in Everything
└──▷ BREAKING ON UPGRADE
! Cloudflare MCP product-specific servers no longer serve /sse; any MCP client still configured with an /sse URL must be updated to /mcp.
API surface changed: +1 endpoint, 14 modified︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
API change API surface changed: +1 endpoint, 14 modified︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
+ POST /accounts/{account_id}/managed-defense/vulnerability-discovery/repos/{repo_id}/token
~ DELETE /accounts/{account_id}/mnm/config: request body changed ~ DELETE /accounts/{account_id}/mnm/rules/{rule_id}: request body changed ~ DELETE /accounts/{account_id}/workers/observability/destinations/{slug}: response schema changed ~ GET /accounts/{account_id}/managed-defense/vulnerability-discovery/repos/{repo_id}/scans/{scan_id}/report: response schema changed ~ GET /accounts/{account_id}/managed-defense/vulnerability-discovery/scans/{scan_id}/report: response schema changed ~ GET /accounts/{account_id}/one/applications/{application_id}/setup-flows: response schema changed ~ GET /accounts/{account_id}/pipelines/v1/sinks: param direction (query) added; param order_by (query) added ~ GET /accounts/{account_id}/pipelines/v1/streams: param direction (query) added; param order_by (query) added ~ GET /accounts/{account_id}/workers/observability/destinations: response schema changed ~ PATCH /accounts/{account_id}/mnm/rules/{rule_id}/advertisement: request body changed ~ PATCH /accounts/{account_id}/workers/observability/destinations/{slug}: request body changed; response schema changed ~ POST /accounts/{account_id}/managed-defense/vulnerability-discovery/scans: request body changed ~ POST /accounts/{account_id}/workers/observability/destinations: response schema changed ~ PUT /accounts/{account_id}/workflows/{workflow_name}: response schema changed
New endpoint POST /accounts/{account_id}/managed-defense/vulnerability-discovery/repos/{repo_id}/token︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GET /accounts/{account_id}/pipelines/v1/sinks: param direction (query) added; param order_by (query) added GET /accounts/{account_id}/pipelines/v1/streams: param direction (query) added; param order_by (query) added
3 details in Everything
Cloudflare Workers AI adds Clairic (typed forecasting model) and DeepSeek-V4.1-Flash (552B MoE MoE A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token. multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats.
Adds clairic to Workers AI — a System One-style model that extracts, computes, estimates, and forecasts strongly typed values with confidence scores and probabilities; currently in preview.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds deepseek-v4.1-flash-1017 to Workers AI — a multimodal Mixture-of-Experts Mixture-of-Experts A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token.
2 details in Everything
Cloudflare feature flags now support attribute-based targeting rules with 13 comparison operators and AND/OR logic.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Cloudflare adds Clairic extraction model and DeepSeek V4.1 Flash 1017 to Workers AI, step-up MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds @cf/cloudflare/clairic to Workers AI (preview): an extraction model returning typed values (text, number, date, duration, list, estimate, forecast) with p_null, confidence, and optional quantiles; $0.10/M input tokens, no output charge. Adds @cf/deepseek-ai/deepseek-v4.1-flash-1017 to Workers AI: multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. MoE MoE A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token. function calling function calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions. reasoning_effort. Cloudflare API MCP server gains step-up authorization: start with Minimal scopes and approve additional scopes on demand when an insufficient_scope challenge is returned. wrangler deploy, wrangler versions upload, and wrangler preview upload source maps by default from Wrangler 4.150.0; opt out with upload_source_maps = false.Think Agent Skills migrate to @cloudflare/computer Workspace with JavaScriptWorkerBackend; @cloudflare/shell and createExecuteTool are deprecated with no automatic data migration.
5 details in Everything
└──▷ BREAKING ON UPGRADE
! @cloudflare/shell is deprecated and createExecuteTool will no longer be developed or supported; existing workspace data is not migrated automatically to @cloudflare/computer tables.
Cloudflare Workers source maps now upload by default; API MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Wrangler and cf now upload source maps by default, pointing Workers stack traces at original source without any configuration.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Cloudflare API MCP server now supports step-up authorization, allowing agents to grant only required scopes at connect time and authorize additional scopes on demand. Think and Agent Skills now use @cloudflare/computer for their workspace; @cloudflare/shell is deprecated.
Wrangler and cf now upload source maps by default, pointing Workers stack traces at original source without any configuration.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Cloudflare API MCP server now supports step-up authorization, allowing agents to grant only required scopes at connect time and authorize additional scopes on demand.
1 more in Everything
└──▷ BREAKING ON UPGRADE
! @cloudflare/shell is deprecated; Think agents and Agent Skills have migrated to @cloudflare/computer for their workspace.
WAF - WAF Release - 2026-10-21 - Emergency - Cloudflare Free Ruleset (2026-10-21)
Oct 21, 2026
·
issue 115
WAF - WAF Release - 2026-10-21 - Emergency - Cloudflare Managed Ruleset (2026-10-21)
Oct 21, 2026
·
issue 115
Cloudflare: Adds Workers AI models @cf/cloudflare/clairic (extraction, $0.10/M input tokens) and @cf/deepseek-ai/deepseek-v4.1-flash-1017 (552B multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. MoE MoE A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token.
└──▷ TRY IT
Find documentation on rate limiting from the terminal without opening a browser — useful for quick lookups during incident response or agent-assisted scripting.
copy
$ cf docs search "rate limit requests with WAF" Trigger a specific Worker's scheduled handler on demand during local development to validate cron logic without waiting for a schedule or constructing raw URLs.
copy
$ curl -X POST "http://localhost:8787/cdn-cgi/local/explorer/api/local/scheduled?worker=my-worker" -H 'Content-Type: application/json' -d '{"cron":"0 * * * *","scheduled_time":1745856238000}' Extract typed structured values from unstructured invoice text using Clairic — avoiding brittle regex or LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code.
copy
$ curl https://api.cloudflare.com/client/v4/accounts/<account_id>/ai/run/@cf/cloudflare/clairic \
-H 'Authorization: Bearer <token>' \
-H 'Content-Type: application/json' \
-d '{
"model": "clairic",
"state": "Invoice INV-2291 from Northwind Supply, issued 2026-09-02, net 30. 4 pallets at $250.00 each, shipping $80.00. Contact: Dana Ruiz, Priya Shah.",
"fields": {
"invoice_number": {"type": "text"},
"issued": {"type": "date"},
"due_date": {"type": "date", "description": "Issue date plus the net payment days"},
"total": {"type": "number", "decimals": 2, "unit": "USD", "description": "Amount due including shipping"},
"contacts": {"type": "list", "items": "text"}
}
}'
Adds step-up authorization to the Cloudflare API MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. insufficient_scope challenge naming the required scope when a tool call needs one not yet granted; choose Minimal on the consent page to start with least access. Improves Precursor (bot detection): the Status dropdown in Settings now offers Off , Monitor , and Arm modes, where Monitor runs Precursor detections without affecting bot score or Challenge clearance and Arm enables full enforcement; also adds a Show Interstitial site-wide default and Interstitial Rules per-request overrides, decoupling the Precursor Interstitial from the detection mode. Adds Local Explorer support for Cron Triggers: a POST /cdn-cgi/local/explorer/api/local/scheduled?worker=<worker-name> API endpoint accepting a JSON body with cron and optional scheduled_time (epoch ms), available via wrangler dev, cf dev, or the Cloudflare Vite plugin; and a Cron Triggers panel in the Local Explorer UI at /cdn-cgi/local/explorer supporting ad hoc cron expression building, configured expression invocation, reusable scheduled time presets, and noRetry() outcome inspection, without modifying cloudflare.config.ts or deployed triggers.
Adds step-up authorization to the Cloudflare API MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. insufficient_scope challenge naming the required scope when a tool call needs one not yet granted; choose Minimal on the consent page to start with least access. Adds Local Explorer support for Cron Triggers: a POST /cdn-cgi/local/explorer/api/local/scheduled?worker=<worker-name> API endpoint accepting a JSON body with cron and optional scheduled_time (epoch ms), available via wrangler dev, cf dev, or the Cloudflare Vite plugin; and a Cron Triggers panel in the Local Explorer UI at /cdn-cgi/local/explorer supporting ad hoc cron expression building, configured expression invocation, reusable scheduled time presets, and noRetry() outcome inspection, without modifying cloudflare.config.ts or deployed triggers.
1 more in Everything
Cloudflare adds Cloud Workload Security beta, Precursor Monitor mode, Cron Trigger local testing, CJK keyword search, cf docs search, and 50k Tunnel routes︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Search Cloudflare docs from the terminal and retrieve the top result as Markdown — useful when working with a coding agent or in a shell-only environment.
copy
$ url=$(cf docs search "rate limit requests with WAF" | jq -r '.[0].url')
curl -H "Accept: text/markdown" "$url" Trigger a Worker's scheduled() handler on demand during local development without constructing URLs manually — useful for CI or agent-driven test harnesses.
copy
$ curl -X POST "http://localhost:8787/cdn-cgi/local/explorer/api/local/scheduled?worker=my-worker" \
-H 'Content-Type: application/json' \
-d '{"cron":"0 * * * *","scheduled_time":1745856238000}' Enable CJK keyword search for an AI Search index whose content is in Japanese, Chinese, or Korean — note that changing this setting triggers a full reindex.
yaml
copy
keyword_tokenizer: trigram
Adds cf docs search subcommand in Cloudflare CLI 1.0.0-beta.16 to search live Cloudflare documentation from the terminal or a coding agent, returning up to five ranked JSON results (title, description, URL) per query.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds keyword_tokenizer: trigram support to AI Search keyword search, enabling Japanese, Chinese, and Korean natural-language queries; changing the tokenizer triggers a full reindex. Adds cf docs search shell integration with jq and Accept: text/markdown header to fetch full documentation pages as Markdown from agent-parsed search results. Launches Cloud Workload Security (CWS) in Beta, allowing policy controls on cloud API requests (including Rego checks and request filters) enforced via a CWS proxy before requests reach the cloud provider; requires a Zero Trust subscription. Raises the default Cloudflare Tunnel routes limit to 50,000 per account (up from 1,000), covering CIDR CIDR A notation for a block of IP addresses, such as 10.0.0.0/24. The number after the slash says how many leading address bits identify the network. cloudflared.
+2 more
show less
Introduces Tunnels for Platforms, enabling accounts to purchase more than 1,000 tunnels at $4.50 per tunnel per month via Tunnels > Buy more tunnels in the dashboard. Updates Workers Builds default runtimes with environment-variable overrides: NODE_VERSION, PYTHON_VERSION, RUBY_VERSION, GO_VERSION, BUN_VERSION, and YARN_VERSION; Bun 1.4.3 supports both bun.lockb (v1) and bun.lock (v2) lockfiles.
Adds cf docs search subcommand in Cloudflare CLI 1.0.0-beta.16 to search live Cloudflare documentation from the terminal or a coding agent, returning up to five ranked JSON results (title, description, URL) per query.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Launches Cloud Workload Security (CWS) in Beta, allowing policy controls on cloud API requests (including Rego checks and request filters) enforced via a CWS proxy before requests reach the cloud provider; requires a Zero Trust subscription. Introduces Tunnels for Platforms, enabling accounts to purchase more than 1,000 tunnels at $4.50 per tunnel per month via Tunnels > Buy more tunnels in the dashboard.
4 more in Everything
└──▷ BREAKING ON UPGRADE
! Cloudflare CLI 1.0.0-beta.16 standardizes generated command names to kebab-case — for example, cf accounts billing getCredits is renamed to cf accounts billing get-credits. Any script or automation using camelCase command names will break.
Cloudflare API adds DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
└──▷ TRY IT
Consume a batch of records from a Data streaming subscription in a pipeline script.
copy
$ curl -X POST 'https://api.cloudflare.com/subscriptions/{subscription_id}/consume' \
-H 'Authorization: Bearer <token>' Acknowledge a processed batch so the broker advances the offset and does not redeliver it.
copy
$ curl -X POST 'https://api.cloudflare.com/subscriptions/{subscription_id}/batches/{batch_id}/ack' \
-H 'Authorization: Bearer <token>'
Adds GET /accounts/{account_id}/dlp/validators and GET /accounts/{account_id}/dlp/validators/{validator_id} endpoints to list and retrieve DLP validators.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds full CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. GET|POST /accounts/{account_id}/dlp/validators/proximity_words and GET|PUT|DELETE /accounts/{account_id}/dlp/validators/proximity_words/{validator_id}. Adds POST /produce endpoint to publish records to the new Data streaming API. Adds subscription management endpoints: GET|POST /subscriptions, GET|DELETE /subscriptions/{subscription_id}, and POST /subscriptions/{subscription_id}/consume for consuming records. Adds batch lifecycle endpoints: POST /subscriptions/{subscription_id}/batches/{batch_id}/ack to acknowledge, POST /subscriptions/{subscription_id}/batches/{batch_id}/nack to release, and POST /subscriptions/{subscription_id}/batches/{batch_id}/extend to extend a batch lease.
+1 more
show less
Documents that cloudflare_organization Terraform resource requires a Global API key for read, update, and delete operations — User API tokens only support list and create.
Adds GET /accounts/{account_id}/dlp/validators and GET /accounts/{account_id}/dlp/validators/{validator_id} endpoints to list and retrieve DLP validators.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds full CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. GET|POST /accounts/{account_id}/dlp/validators/proximity_words and GET|PUT|DELETE /accounts/{account_id}/dlp/validators/proximity_words/{validator_id}. Adds POST /produce endpoint to publish records to the new Data streaming API. Adds subscription management endpoints: GET|POST /subscriptions, GET|DELETE /subscriptions/{subscription_id}, and POST /subscriptions/{subscription_id}/consume for consuming records. Adds batch lifecycle endpoints: POST /subscriptions/{subscription_id}/batches/{batch_id}/ack to acknowledge, POST /subscriptions/{subscription_id}/batches/{batch_id}/nack to release, and POST /subscriptions/{subscription_id}/batches/{batch_id}/extend to extend a batch lease.
1 more in Everything
Cloudflare adds Cloud Workload Security for applying request-level policies to cloud API traffic via an in-environment proxy.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Cloudflare: Adds cf docs search in Cloudflare CLI 1.0.0-beta.16 to find Cloudflare guides and examples from the terminal.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Search Cloudflare documentation without leaving the terminal during an incident or local dev session.
copy
$ cf docs search 'tunnel route limit'
Raises the default route limit for Cloudflare Tunnel and Cloudflare Mesh to 50,000 per account, and enables purchasing more than 1,000 tunnels per account via Tunnels for Platforms. Enables Local Explorer to invoke configured or ad hoc Cron Triggers with custom scheduled times during local development.
2 more in Everything
Cloudflare: Supports custom applications in the Application Library, referenceable in Gateway DNS, Network, and HTTP policies.
└──▷ TRY IT
Search Cloudflare documentation without leaving the terminal during an incident or review.
copy
$ cf docs search 'tunnel route limit' Fire a Cron Trigger at an arbitrary scheduled time locally to verify time-sensitive job logic before deploying.
📍 In the Local Explorer UI, select your Worker, choose Cron Triggers , enter a custom scheduled time, and click Invoke .
Enables Cloudflare Workers to validate data loss prevention matches by adjusting confidence or rejecting matches from custom pattern entries.
1 detail in Everything
Bots - Precursor adds Monitor mode (2026-10-19)
Oct 19, 2026
·
issue 113
Cloudflare Precursor gains Monitor mode and a decoupled Interstitial Rules system for safer bot-score testing.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
Safely evaluate Precursor detections on live traffic before they impact bot scores or block users.
📍 In the Cloudflare dashboard, go to Security › Settings, open the Precursor Status dropdown, and select Monitor . Precursor detections will run but bot score and Challenge clearance remain unchanged.
Require an interstitial Challenge only on sensitive paths (e.g. checkout) while keeping the rest of the site unaffected.
📍 In Security › Settings, set Show Interstitial to off (sitewide default), then add an Interstitial Rules entry matching the path /checkout with the interstitial Challenge enabled.
Adds Monitor option to the Precursor Status dropdown (under Security > Settings), letting traffic run through Precursor detections without affecting bot score or Challenge clearance.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Arm option to the Precursor Status dropdown so that Precursor detections actively affect bot score and Challenge clearance when ready for production. Decouples the Precursor Interstitial from the Precursor mode: set a sitewide default with Show Interstitial , then override per-path with Interstitial Rules (e.g. enforce an interstitial Challenge on /checkout while leaving it off elsewhere).
3 details in Everything
API surface changed: +21 endpoints, −3 endpoints, 45 modified︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
API change API surface changed: +21 endpoints, −3 endpoints, 45 modified︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
+ DELETE /accounts/{account_id}/data-security/posture/finding_types/{finding_type_id} + DELETE /accounts/{account_id}/dlp/validators/proximity_words/{validator_id} + DELETE /accounts/{account_id}/dlp/validators/worker/{validator_id} + GET /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/{priority_id}/matches + GET /accounts/{account_id}/data-security/posture/asset_schemas + GET /accounts/{account_id}/data-security/posture/asset_schemas/{asset_class} + GET /accounts/{account_id}/dlp/validators + GET /accounts/{account_id}/dlp/validators/proximity_words + GET /accounts/{account_id}/dlp/validators/proximity_words/{validator_id} + GET /accounts/{account_id}/dlp/validators/worker + GET /accounts/{account_id}/dlp/validators/worker/{validator_id} + GET /accounts/{account_id}/dlp/validators/worker/{validator_id}/status + GET /accounts/{account_id}/dlp/validators/{validator_id} + PATCH /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/{priority_id}/matches + POST /accounts/{account_id}/data-security/posture/finding_types + POST /accounts/{account_id}/data-security/posture/finding_types/validate + POST /accounts/{account_id}/dlp/validators/proximity_words + POST /accounts/{account_id}/dlp/validators/worker + PUT /accounts/{account_id}/data-security/posture/finding_types/{finding_type_id} + PUT /accounts/{account_id}/dlp/validators/proximity_words/{validator_id} + PUT /accounts/{account_id}/dlp/validators/worker/{validator_id}
~ DELETE /accounts/{account_id}/diagnostics/endpoint-healthchecks/{id}: response schema changed ~ GET /accounts/{account_id}/browser-rendering/crawl/{job_id}: response schema changed ~ GET /accounts/{account_id}/cni/cnis: response schema changed ~ GET /accounts/{account_id}/data-security/posture/finding_types: param direction (query) added; param max_updated_at (query) added; param min_updated_at (query) added; param order (query) added; param origins (query) added; param quarantined (query) added; param severities (query) added; param types (query) added; response schema changed ~ GET /accounts/{account_id}/diagnostics/endpoint-healthchecks: response schema changed ~ GET /accounts/{account_id}/diagnostics/endpoint-healthchecks/{id}: response schema changed ~ GET /accounts/{account_id}/dns_records/usage: response schema changed ~ GET /accounts/{account_id}/email-security/settings/allow_policies: param expired (query) added ~ GET /accounts/{account_id}/email-security/settings/block_senders: param expired (query) added ~ GET /accounts/{account_id}/email-security/settings/content_policies: param expired (query) added ~ GET /accounts/{account_id}/resource-library/applications: param cursor (query) added ~ GET /accounts/{account_id}/resource-library/categories: param cursor (query) added; response schema changed ~ GET /zones/{zone_id}/dns_records: response schema changed ~ GET /zones/{zone_id}/dns_records/usage: response schema changed ~ GET /zones/{zone_id}/dns_records/{dns_record_id}: response schema changed ~ PATCH /accounts/{account_id}/devices/policy: request body changed ~ PATCH /accounts/{account_id}/devices/policy/{policy_id}: request body changed ~ PATCH /accounts/{account_id}/devices/posture/integration/{integration_id}: request body changed ~ PATCH /accounts/{account_id}/email/sending/suppressions/{suppression_id}: request body changed ~ PATCH /zones/{zone_id}/dns_records/{dns_record_id}: response schema changed ~ POST /accounts/{account_id}/ai-gateway/billing/topup/config: request body changed; response schema changed ~ POST /accounts/{account_id}/ai-search/instances: response schema changed ~ POST /accounts/{account_id}/ai-search/instances/{id}/jobs: response schema changed ~ POST /accounts/{account_id}/ai-search/namespaces/{namespace}/instances: response schema changed ~ POST /accounts/{account_id}/ai-search/namespaces/{namespace}/instances/{id}/jobs: response schema changed ~ POST /accounts/{account_id}/ai-search/namespaces/{namespace}/instances/{id}/purge_cache: response schema changed ~ POST /accounts/{account_id}/cloudforce-one/v2/priority-intelligence: request body changed ~ POST /accounts/{account_id}/cws/policies: request body changed ~ POST /accounts/{account_id}/devices/networks: request body changed ~ POST /accounts/{account_id}/devices/policy: request body changed ~ POST /accounts/{account_id}/devices/posture/integration: request body changed ~ POST /accounts/{account_id}/diagnostics/endpoint-healthchecks: response schema changed ~ POST /accounts/{account_id}/diagnostics/traceroute: request body changed; response schema changed ~ POST /accounts/{account_id}/dlp/entries: request body changed ~ POST /zones/{zone_id}/dns_records: response schema changed ~ POST /zones/{zone_id}/dns_records/import: response schema changed ~ POST /zones/{zone_id}/dns_records/scan: response schema changed ~ POST /zones/{zone_id}/dns_records/scan/trigger: response schema changed ~ PUT /accounts/{account_id}/ai-search/instances/{id}: response schema changed ~ PUT /accounts/{account_id}/ai-search/namespaces/{namespace}/instances/{id}: response schema changed ~ PUT /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/{priority_id}: request body changed; response schema changed ~ PUT /accounts/{account_id}/cws/policies/{policy_id}: request body changed ~ PUT /accounts/{account_id}/devices/networks/{network_id}: request body changed ~ PUT /accounts/{account_id}/diagnostics/endpoint-healthchecks/{id}: response schema changed ~ PUT /zones/{zone_id}/dns_records/{dns_record_id}: response schema changed
− GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds (breaking) − GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/health (breaking) − PATCH /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds/opt-out (breaking)
New endpoint DELETE /accounts/{account_id}/data-security/posture/finding_types/{finding_type_id}︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New endpoint DELETE /accounts/{account_id}/dlp/validators/proximity_words/{validator_id} New endpoint DELETE /accounts/{account_id}/dlp/validators/worker/{validator_id} New endpoint GET /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/{priority_id}/matches New endpoint GET /accounts/{account_id}/data-security/posture/asset_schemas
+5 more
show less
New endpoint GET /accounts/{account_id}/data-security/posture/asset_schemas/{asset_class} New endpoint GET /accounts/{account_id}/dlp/validators New endpoint GET /accounts/{account_id}/dlp/validators/proximity_words New endpoint GET /accounts/{account_id}/dlp/validators/proximity_words/{validator_id} New endpoint GET /accounts/{account_id}/dlp/validators/worker
10 details in Everything
└──▷ BREAKING ON UPGRADE
! Removed endpoint GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds! Removed endpoint GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/health! Removed endpoint PATCH /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds/opt-out
API surface changed: +96 endpoints, −24 endpoints, 177 modified︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
New endpoint DELETE /accounts/{account_id}/access/user_populations/{user_population_id}/users/{user_id}︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New endpoint DELETE /accounts/{account_id}/ai-search/namespaces/{namespace}/instances/{id} New endpoint DELETE /accounts/{account_id}/ai-search/namespaces/{namespace}/instances/{id}/items/{item_id} New endpoint DELETE /accounts/{account_id}/cws/basic-auth-credentials/{credential_id} New endpoint DELETE /accounts/{account_id}/cws/basic-auth-credentials/{credential_id}/secrets/{secret_id}
+5 more
show less
New endpoint DELETE /accounts/{account_id}/cws/deployments/{deployment_id} New endpoint DELETE /accounts/{account_id}/cws/domain-acls/{domain_acl_id} New endpoint DELETE /accounts/{account_id}/cws/policies/{policy_id} New endpoint DELETE /accounts/{account_id}/cws/policy-sets/{policy_set_id} New endpoint DELETE /accounts/{account_id}/cws/rego-metadata/{rego_metadata_id}
10 details in Everything
└──▷ BREAKING ON UPGRADE
! Removed endpoint DELETE /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}! Removed endpoint DELETE /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/items/{item_id}! Removed endpoint GET /accounts/{account_id}/ai-search/namespaces/{name}/instances! Removed endpoint GET /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}! Removed endpoint GET /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/items! Removed endpoint GET /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/items/{item_id}! Removed endpoint GET /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/items/{item_id}/chunks! Removed endpoint GET /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/items/{item_id}/download! Removed endpoint GET /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/items/{item_id}/logs! Removed endpoint GET /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/jobs! Removed endpoint GET /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/jobs/{job_id}! Removed endpoint GET /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/jobs/{job_id}/logs! Removed endpoint GET /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/stats! Removed endpoint PATCH /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}! Removed endpoint PATCH /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/items/{item_id}! Removed endpoint PATCH /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/jobs/{job_id}! Removed endpoint POST /accounts/{account_id}/ai-search/namespaces/{name}/instances! Removed endpoint POST /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/chat/completions! Removed endpoint POST /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/items! Removed endpoint POST /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/jobs! Removed endpoint POST /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/purge_cache! Removed endpoint POST /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/search! Removed endpoint PUT /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}! Removed endpoint PUT /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/items! GET /zones/{zone_id}/precursor: param Cloudflare-Version (header) added [required]! PUT /zones/{zone_id}/precursor: param Cloudflare-Version (header) added [required]; request body changed
Cloudflare adds Advanced Custom Nameserver sets (beta), trim functions for Rules, DNS64 DNS64 A DNS server mechanism that synthesizes AAAA (IPv6) records from A (IPv4) records, letting IPv6-only clients reach IPv4-only hosts without dual-stack infrastructure. Cyber tools use it to handle mixed-protocol environments transparently. EDNS EDNS An extension to the DNS protocol, standardized by the IETF, that adds larger UDP payload sizes, option flags, and extensible fields; cyber tools use it to carry additional query metadata and avoid fragmentation issues. RUM RUM Real User Monitoring — a technique that collects performance and behaviour data from actual users' browsers or clients in production, giving cyber tools visibility into real-world latency and errors rather than synthetic test results. LCP LCP Link Control Protocol, part of PPP, negotiates and configures point-to-point data links between two peers. Cyber tools targeting PPP-based connections use it to inspect or manipulate link establishment.
Adds nameserver_set_id field to PATCH /zones/{zone_id}/dns_settings and a new POST /accounts/{account_id}/dns_settings/nameserver_sets endpoint to create reusable Advanced Custom Nameserver sets (beta, Enterprise), supporting up to 3 IPv4 and 3 IPv6 IPv6 The current version of the Internet Protocol, standardized by the IETF, using 128-bit addresses to replace the exhausted IPv4 space. Cyber tools target it because modern networks run dual-stack or IPv6-only. advanced: true flag to allocate from Advanced anycast network groups. Adds trim() , trim_start() , and trim_end() functions to Cloudflare Rules for stripping surrounding bytes (ASCII whitespace by default, or a custom byte string) from request values before comparison — available on all HTTP products and all plans. Adds Enable DNS64 toggle for Gateway DNS locations and support for requesting DNS64 via EDNS option in individual queries, enabling AAAA record synthesis from A records for IPv6-only/NAT64 networks across UDP UDP A network protocol that sends individual messages without guaranteeing delivery or order. Applications trade built-in reliability for less overhead and can add their own recovery. TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. DoT DoT DNS over TLS: an IETF standard (RFC 7858) that wraps DNS queries in a TLS session on port 853, preventing eavesdropping and tampering that plain UDP DNS allows. DoH DoH DNS over HTTPS, an IETF standard (RFC 8484) that tunnels DNS queries inside encrypted HTTPS traffic, making resolution indistinguishable from web traffic and bypassing traditional DNS-based monitoring. Adds configurable session duration for infrastructure applications (default 24 hours), settable via the dashboard or API; when the duration elapses, active SSH connections are closed and users must reconnect. Audit Logs v2 now captures view actions (corresponding to GET requests) for supported endpoints; excluded from the dashboard by default via an Action type is not view filter, but always available via the Audit Logs v2 API and Logpush.
+1 more
show less
Real User Monitoring (RUM) in Web Analytics now breaks down Largest Contentful Paint (LCP) and Interaction to Next Paint (INP) into sub-parts, and splits connection time into TCP and TLS, queryable through the GraphQL Analytics API at P25, P50, P75, P90, P95, P99, and P999 percentiles (values in microseconds).
6 details in Everything
Cloudflare: Adds endpoints to manage Rego modules in Cloud Workload Security, including GET/POST /accounts/{account_id}/cws/rego-modules
└──▷ TRY IT
Audit all Just-in-Time access requests to review who requested elevated access and when.
copy
$ curl -s -X GET 'https://api.cloudflare.com/client/v4/accounts/<account_id>/access/logs/jit_requests' \
-H 'Authorization: Bearer <token>' \
-H 'Content-Type: application/json' Remove a compromised or lost MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone.
copy
$ curl -s -X DELETE 'https://api.cloudflare.com/client/v4/accounts/<account_id>/access/users/<user_id>/mfa_authenticators/<authenticator_id>' \
-H 'Authorization: Bearer <token>'
Adds GET/POST /accounts/{account_id}/cws/tenant-structures and GET/PUT/DELETE /accounts/{account_id}/cws/tenant-structures/{structure_id} endpoints for managing CWS tenant structures. Adds GET/POST /accounts/{account_id}/cws/tenant-structures/{structure_id}/nodes, GET/PUT/DELETE .../nodes/{node_id}, and POST .../nodes/batch endpoints for managing and batch-mutating nodes within a CWS tenant structure.
2 details in Everything
Cloudflare: Enables DNS64 DNS64 A DNS server mechanism that synthesizes AAAA (IPv6) records from A (IPv4) records, letting IPv6-only clients reach IPv4-only hosts without dual-stack infrastructure. Cyber tools use it to handle mixed-protocol environments transparently. EDNS EDNS An extension to the DNS protocol, standardized by the IETF, that adds larger UDP payload sizes, option flags, and extensible fields; cyber tools use it to carry additional query metadata and avoid fragmentation issues.
└──▷ TRY IT
Strip leading and trailing whitespace from a request header value before matching it in a WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
copy
$ trim(http.request.headers["x-custom-header"])
Adds nameserver sets for Advanced Custom Nameservers (beta), allowing standard or advanced account-level sets to be created and assigned to zones via the DNS settings API.
1 detail in Everything
Cloudflare adds configurable session duration for infrastructure apps, DNS64 DNS64 A DNS server mechanism that synthesizes AAAA (IPv6) records from A (IPv4) records, letting IPv6-only clients reach IPv4-only hosts without dual-stack infrastructure. Cyber tools use it to handle mixed-protocol environments transparently.
Adds trim() , trim_start() , and trim_end() functions to Rules expressions for removing whitespace or custom bytes from the ends of request values. Supports configuring DNS64 per Gateway DNS location or requesting synthesis per query with an empty EDNS EDNS An extension to the DNS protocol, standardized by the IETF, that adds larger UDP payload sizes, option flags, and extensible fields; cyber tools use it to carry additional query metadata and avoid fragmentation issues. Adds view-action capture to Audit Logs v2, surfacing records through the API, Logpush, and dashboard. Adds configurable session duration to infrastructure applications in Cloudflare One, defaulting to 24 hours. Adds support for creating standard or Advanced account-level nameserver sets and assigning them to zones via the DNS settings API (beta).
5 details in Everything
WAF - WAF Release - 2026-10-14 - Emergency (2026-10-14)
Oct 14, 2026
·
issue 109
Cloudflare adds MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. LCP LCP Link Control Protocol, part of PPP, negotiates and configures point-to-point data links between two peers. Cyber tools targeting PPP-based connections use it to inspect or manipulate link establishment. RUM RUM Real User Monitoring — a technique that collects performance and behaviour data from actual users' browsers or clients in production, giving cyber tools visibility into real-world latency and errors rather than synthetic test results.
Adds browserTool to the Agents SDK — a persistent browser that retains tabs and logins between turns, with adapters for Pi Durable, AI SDK, and TanStack AI.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Cloudflare API MCP server now streams Workers Issues as MCP events, enabling MCP clients to subscribe and receive each new issue in real time. Real User Monitoring in Cloudflare Web Analytics now breaks LCP and INP into sub-part metrics and splits connection time into TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. Workers subrequests to Cloudflare-proxied BYOIP BYOIP Bring Your Own IP — a cloud provider feature letting customers move their own publicly routable IP blocks into the provider's network, so traffic to those addresses routes through the cloud without renumbering.
Adds browserTool to the Agents SDK — a persistent browser that retains tabs and logins between turns, with adapters for Pi Durable, AI SDK, and TanStack AI.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Cloudflare API MCP server now streams Workers Issues as MCP events, enabling MCP clients to subscribe and receive each new issue in real time.
2 more in Everything
Workers, BYOIP, Bots - Workers subrequests now preserve context for BYOIP destinations (2026-10-13)
Oct 13, 2026
·
issue 107
Workers subrequests to BYOIP BYOIP Bring Your Own IP — a cloud provider feature letting customers move their own publicly routable IP blocks into the provider's network, so traffic to those addresses routes through the cloud without renumbering. CF-Worker header and cf.worker.upstream_zone, fixing Bot Management and security rule evaluation.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Workers subrequests to BYOIP-proxied hostnames now preserve the CF-Worker header and cf.worker.upstream_zone field, ensuring consistent security rule evaluation across same-zone and cross-zone subrequests.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Bot Management fields on destination zones — including bot scores, verified bot status, and JA3 JA3 A method for fingerprinting TLS clients by hashing fields from the ClientHello message, producing a short string that identifies the TLS library or application making a connection regardless of IP or port. JA4 JA4 A network fingerprinting method that hashes observable TLS handshake fields into a short, readable tag, giving cyber tools a stable, version-agnostic way to classify clients and detect anomalies.
Workers subrequests to BYOIP-proxied hostnames now preserve the CF-Worker header and cf.worker.upstream_zone field, ensuring consistent security rule evaluation across same-zone and cross-zone subrequests.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
1 more in Everything
Agents SDK gains web_fetch and web_search tools; Queues adds EU/US/FedRAMP FedRAMP A US government program that standardizes cloud security authorization, letting vendors get a single assessment accepted across federal agencies instead of repeating the process for each one.
└──▷ TRY IT
Create a GDPR GDPR EU regulation enacted in 2018 that governs how organizations collect, store, and process personal data of EU residents, giving cyber tools legal obligations around data handling and breach notification.
copy
$ wrangler queues create --queue-name my-eu-queue --jurisdiction eu Provision an EU-jurisdiction queue via the API, for automated infrastructure pipelines.
copy
$ curl -X POST https://api.cloudflare.com/client/v4/accounts/<account_id>/queues \
-H 'Authorization: Bearer <token>' \
-H 'Content-Type: application/json' \
-d '{"queue_name": "my-eu-queue", "jurisdiction": "eu"}' Trigger an on-demand API Shield schema learning run immediately after sending representative traffic during testing, without waiting for the weekly schedule.
📍 In the Cloudflare dashboard, go to Web Assets › Operations, open the More options menu on the operations table, select Ad-hoc learn schema , then select Run learning in the Schema learning dialog.
Adds web_fetch (Agents SDK v0.28.0+, importable from agents/webfetch/pi) for reading webpages, PDFs, and supported Office documents with automatic Markdown conversion, exposing fetchWeb() , windowWebFetchPage() , and renderWebFetchPage() for direct fetching without a model or Durable Object; and web_search (Agents SDK v0.27.0+, importable from agents/websearch/pi) for querying the public web via the Cloudflare Web Search API (powered by ceramic.ai, Exa, and Linkup), exposing createAIWebSearch() and createHTTPWebSearch() for model-free search.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds OpenCodeHarness (experimental) to the Agents SDK, enabling OpenCode 2.0 to run inside a plain Durable Object with SQLite sessions, Lifecycle jobs, and Workers AI model binding via the agents/models/opencode provider; requires agents@latest @opencode/sdk@2 @opencode/plugin@2. Adds jurisdictional restrictions to Cloudflare Queues via the --jurisdiction flag (Wrangler) and jurisdiction parameter on the POST /queues API endpoint; supported values are eu (European Union), us (United States), and fedramp (FedRAMP-Moderate data centers). Adds skills/list discovery and skill://<name>/<path> file access to the Cloudflare API MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. https://mcp.cloudflare.com/mcp, serving Cloudflare skills via the Skills over MCP extension. Adds unified navigation combining Zero Trust and main Cloudflare dashboard navigation, giving Zero Trust customers access to developer platform, account memberships, and resource tagging from a single sidebar; Zero Trust Network items replaced by experiences under Networking , and Resolvers & Proxies moved under Traffic Controls.
+2 more
show less
Extends the Workers runtime update grace period for pending requests and connections from 30 seconds to up to 20 minutes, covering long-running HTTP requests, streamed AI responses, and live WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output. Raises the Markdown for Agents HTML conversion limit from 2 MiB to 6 MiB (6,291,456 bytes) of decompressed HTML, and switches to an in-process streaming engine at the edge.
Adds web_fetch (Agents SDK v0.28.0+, importable from agents/webfetch/pi) for reading webpages, PDFs, and supported Office documents with automatic Markdown conversion, exposing fetchWeb() , windowWebFetchPage() , and renderWebFetchPage() for direct fetching without a model or Durable Object; and web_search (Agents SDK v0.27.0+, importable from agents/websearch/pi) for querying the public web via the Cloudflare Web Search API (powered by ceramic.ai, Exa, and Linkup), exposing createAIWebSearch() and createHTTPWebSearch() for model-free search.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds OpenCodeHarness (experimental) to the Agents SDK, enabling OpenCode 2.0 to run inside a plain Durable Object with SQLite sessions, Lifecycle jobs, and Workers AI model binding via the agents/models/opencode provider; requires agents@latest @opencode/sdk@2 @opencode/plugin@2. Adds jurisdictional restrictions to Cloudflare Queues via the --jurisdiction flag (Wrangler) and jurisdiction parameter on the POST /queues API endpoint; supported values are eu (European Union), us (United States), and fedramp (FedRAMP-Moderate data centers).
4 more in Everything
└──▷ BREAKING ON UPGRADE
! Converted Markdown for Agents responses no longer emit the x-markdown-tokens and x-original-tokens headers; clients that relied on these values must calculate token counts themselves.! Content-Length is removed from Markdown for Agents converted responses (the body is now streamed); clients that depended on this header must handle its absence.
API Shield adds on-demand schema learning; Workers AI gains Clef-omni multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats.
Adds on-demand, zone-wide schema learning runs in API Shield, with per-operation result review.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Cloudflare API MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Adds R2 bandwidth analytics broken down by the Cloudflare location that served each request. Clef-omni, a new multimodal decision model accepting text, image, audio, and video input, is now available on Workers AI. Markdown for Agents now uses in-process streaming conversion and supports larger HTML pages.
Adds on-demand, zone-wide schema learning runs in API Shield, with per-operation result review.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Cloudflare API MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Clef-omni, a new multimodal decision model accepting text, image, audio, and video input, is now available on Workers AI.
2 more in Everything
API Shield - Run schema learning on demand (2026-10-12)
Oct 12, 2026
·
issue 104
API Shield now supports on-demand schema learning runs, skipping the weekly schedule for faster feedback during testing.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
After sending representative traffic to a newly deployed API endpoint, immediately trigger schema learning rather than waiting up to a week for the scheduled run.
📍 1. In the Cloudflare dashboard, go to Web Assets › Operations.
2. Open the More options menu on the operations table.
3. Select Ad-hoc learn schema .
4. In the Schema learning dialog, select Run learning .
5. Monitor progress in the dialog; review per-operation results in the Learned schema view as they complete.
Adds an Ad-hoc learn schema option in Web Assets > Operations > More options menu, letting you trigger an API Shield schema learning run immediately instead of waiting for the weekly schedule.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ The Schema learning dialog shows current learning status and last completed run for the zone, while the Learned schema view shows per-operation results — both updating live so you can review individual operations while the zone-wide run continues.
Adds an Ad-hoc learn schema option in Web Assets > Operations > More options menu, letting you trigger an API Shield schema learning run immediately instead of waiting for the weekly schedule.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
1 more in Everything
API surface changed: +13 endpoints, −1 endpoint, 32 modified︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
API change API surface changed: +13 endpoints, −1 endpoint, 32 modified︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
+ DELETE /accounts/{account_id}/addressing/address_maps/{address_map_id}/ips + DELETE /accounts/{account_id}/addressing/address_maps/{address_map_id}/zones + DELETE /accounts/{account_id}/workflows/concurrency/{key_id} + GET /accounts/{account_id}/addressing/loa_documents + GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/skills + GET /accounts/{account_id}/workflows/concurrency + GET /accounts/{account_id}/workflows/concurrency/{key_id} + PATCH /accounts/{account_id}/workflows/concurrency/{key_id} + POST /accounts/{account_id}/addressing/address_maps/{address_map_id}/ips + POST /accounts/{account_id}/addressing/address_maps/{address_map_id}/zones + POST /accounts/{account_id}/browser-extension/config/logs/extension-events/timeseries + POST /accounts/{account_id}/d1/database/{database_id}/undelete + POST /accounts/{account_id}/workflows/concurrency
~ DELETE /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/items/{item_id}: response schema changed ~ DELETE /accounts/{account_id}/storage/kv/namespaces/{namespace_id}: request body changed ~ DELETE /accounts/{account_id}/storage/kv/namespaces/{namespace_id}/values/{key_name}: request body changed ~ DELETE /zones/{zone_id}/dnssec: response schema changed ~ GET /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/items/{item_id}/download: response schema changed ~ GET /accounts/{account_id}/billable/usage: response schema changed ~ GET /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}: response schema changed ~ GET /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/{request_id}: response schema changed ~ GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/skills/{skill_id}/output: response schema changed ~ GET /accounts/{account_id}/workers/domains: param enabled (query) added; param previews_enabled (query) added ~ GET /accounts/{account_id}/workers/observability/usage: param tz (query) added ~ GET /organizations/{organization_id}/billable/usage: response schema changed ~ GET /zones/{zone_id}/dnssec: response schema changed ~ GET /zones/{zone_id}/dnssec/zsk: response schema changed ~ PATCH /zones/{zone_id}/dnssec: response schema changed ~ POST /accounts/{account_id}/addressing/address_maps: response schema changed ~ POST /accounts/{account_id}/addressing/prefixes/{prefix_id}/bgp/prefixes: response schema changed ~ POST /accounts/{account_id}/addressing/prefixes/{prefix_id}/delegations: response schema changed ~ POST /accounts/{account_id}/ai-search/namespaces/{name}/instances/{id}/items: response schema changed ~ POST /accounts/{account_id}/billable/usage: request body changed; response schema changed ~ POST /accounts/{account_id}/browser-extension/config: request body changed ~ POST /accounts/{account_id}/challenges/widgets: request body changed ~ POST /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}: response schema changed ~ POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/skills: request body changed ~ POST /accounts/{account_id}/gateway/locations: request body changed ~ PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{member_account_id}: response schema changed ~ PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/ips/{ip_address}: response schema changed ~ PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/zones/{member_zone_id}: response schema changed ~ PUT /accounts/{account_id}/browser-extension/config: request body changed ~ PUT /accounts/{account_id}/challenges/widgets/{sitekey}: request body changed ~ PUT /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/{request_id}: response schema changed ~ PUT /accounts/{account_id}/gateway/locations/{location_id}: request body changed
− GET /accounts/{account_id}/workflows/{workflow_name}/instances/{instance_id}/subscribe (breaking)
New endpoint DELETE /accounts/{account_id}/addressing/address_maps/{address_map_id}/ips︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New endpoint DELETE /accounts/{account_id}/addressing/address_maps/{address_map_id}/zones New endpoint DELETE /accounts/{account_id}/workflows/concurrency/{key_id} New endpoint GET /accounts/{account_id}/addressing/loa_documents New endpoint GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/skills
+10 more
show less
New endpoint GET /accounts/{account_id}/workflows/concurrency New endpoint GET /accounts/{account_id}/workflows/concurrency/{key_id} New endpoint PATCH /accounts/{account_id}/workflows/concurrency/{key_id} New endpoint POST /accounts/{account_id}/addressing/address_maps/{address_map_id}/ips New endpoint POST /accounts/{account_id}/addressing/address_maps/{address_map_id}/zones New endpoint POST /accounts/{account_id}/browser-extension/config/logs/extension-events/timeseries New endpoint POST /accounts/{account_id}/d1/database/{database_id}/undelete New endpoint POST /accounts/{account_id}/workflows/concurrency GET /accounts/{account_id}/workers/domains: param enabled (query) added; param previews_enabled (query) added GET /accounts/{account_id}/workers/observability/usage: param tz (query) added
15 details in Everything
└──▷ BREAKING ON UPGRADE
! Removed endpoint GET /accounts/{account_id}/workflows/{workflow_name}/instances/{instance_id}/subscribe! POST /accounts/{account_id}/addressing/address_maps: response schema changed! POST /accounts/{account_id}/addressing/prefixes/{prefix_id}/bgp/prefixes: response schema changed! POST /accounts/{account_id}/addressing/prefixes/{prefix_id}/delegations: response schema changed! PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{member_account_id}: response schema changed! PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/ips/{ip_address}: response schema changed! PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/zones/{member_zone_id}: response schema changed
Cloudflare Workers AI adds 14 new models including Cloudflare's own Clef decision model family, Bria image/video tools, and new LLMs LLMs A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code.
└──▷ TRY IT
Run structured multi-question decision-making over a JSON state using Cloudflare's new Clef model — useful for automated triage, policy enforcement, or classification pipelines.
copy
$ curl https://api.cloudflare.com/client/v4/accounts/<ACCOUNT_ID>/ai/run/@cf/cloudflare/clef \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' \
-d '{"state": {"text": "User account has 3 failed logins in 5 minutes from a new country."}, "schema": [{"question": "risk_level", "options": ["low", "medium", "high"]}]}' Remove the background from a product image and get a transparent PNG cutout for use in marketing assets.
copy
$ curl https://api.cloudflare.com/client/v4/accounts/<ACCOUNT_ID>/ai/run/@cf/bria/remove-background \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' \
-d '{"image": "<base64-encoded-image>"}' Generate a 4MP image from a text prompt and capture the returned seed and VGL prompt to reproduce or iterate on the result later.
copy
$ curl https://api.cloudflare.com/client/v4/accounts/<ACCOUNT_ID>/ai/run/@cf/bria/fibo-generate-1.5 \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' \
-d '{"prompt": "A cybersecurity operations center at night, cinematic lighting", "resolution": "4MP", "aspect_ratio": "16:9"}'
Adds clef, clef-flash, and clef-omni — Cloudflare's own multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. MoE MoE A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token. Adds fibo-edit-1.5 from Bria — edits one to four images from a natural-language or structured JSON (VGL) instruction, supporting partial edits via black-and-white mask and multi-image style transfer. Adds fibo-generate-1.5 from Bria — generates images from text prompts or reference images at 1MP or 4MP in nine aspect ratios, returning the seed and VGL prompt used so results can be exactly reproduced or refined. Adds remove-background (Bria RMBG 2.0) — removes image backgrounds and returns a PNG cutout with a transparent background, preserving partial transparency from the input's alpha channel. Adds v-rmbg-3.0 from Bria — removes or replaces the background of video clips up to 60 seconds long with a solid color or transparency; transparent output requires the mov_proresks (ProRes) preset, and output resolution matches the input unless auto_zoom is set.
+5 more
show less
Adds gemini-3.8-flash-tts — Google's flagship text-to-speech model for expressive, natural speech generation. Adds gemini-3.8-flash-lite-tts — a fast, cost-efficient text-to-speech model optimized for high-throughput production workloads. Adds claude-sonnet-5.5 — Anthropic's model combining speed and intelligence with adaptive thinking for coding, tool use tool use A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions. Adds gpt-6.1-sol — OpenAI's Sol model delivering near-Astra performance at lower cost for complex coding, computer use, and professional work. Adds apertus-v1.5-8b (Swiss AI) — an 8B multilingual, multimodal open model supporting contexts up to 262,144 tokens trained exclusively on fully open data.
10 details in Everything
Cloudflare adds cf.appsec.request.failed_detections field, @cf/cloudflare/clef-omni multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. createBatch() for Workflows, and MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
└──▷ USE IT
Block a request only when a security detection itself fails — without altering normal detection verdicts — using the new cf.appsec.request.failed_detections field in a Custom rule expression
text
copy
len(cf.appsec.request.failed_detections) gt 0
Spin up 100 daily-report Workflow instances in a single API call instead of looping, then log any that could not be created
javascript
copy
const { created, errors } = await env.MY_WORKFLOW.createBatch({ count: 100, params: { report: 'daily' } });
for (const error of errors) { console.log(error.index, error.id, error.code, error.message); }
Run a multimodal decision on an installation — checking a photo, an audio clip, and a video clip in one request with @cf/cloudflare/clef-omni
javascript
copy
const response = await env.AI.run('@cf/cloudflare/clef-omni', {
model: 'clef-omni',
state: 'Review the installation: a photo of the unit, an audio recording of it running, and a video of the fan.',
images: ['data:image/png;base64,<base64-png>'],
audio: ['data:audio/mpeg;base64,<base64-mp3>'],
videos: ['data:video/mp4;base64,<base64-mp4>'],
questions: {
label_visible: { type: 'noul', instructions: 'Is the model and serial number label visible in the photo?' },
sounds_normal: { type: 'noul', instructions: 'Does the unit sound like it is running smoothly?' },
fan_running: { type: 'noul', instructions: 'Is the fan running in the video?' }
}
});
Adds cf.appsec.request.failed_detections field (type Array<String>) to Custom rules, Rate limiting rules, and Request Header Transform Rules — returns detection IDs for failures from content scanning, WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. PII PII Personally Identifiable Information — data that can identify a specific individual, such as names, email addresses, or SSNs. Cyber tools flag or redact it to limit exposure and meet privacy regulations. prompt injection prompt injection An attack where text the model reads, such as a web page, file or tool result, carries instructions that override the user's. It is the main security risk for agents with tools. Adds @cf/cloudflare/clef-omni to Workers AI — a 30B-parameter MoE MoE A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token. audio (WAV/MP3), videos (MP4/WebM), images, and text in a single request at $0.150 per million input tokens with a 64K context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. Adds createBatch() options-object form to Cloudflare Workflows, creating up to 100 instances in one call via count (shared options, generated IDs) or instances (per-instance IDs and params); requires Wrangler 4.148.0 or later for local dev and wrangler types Cloudflare API MCP server now exposes Cloudflare skills via the Skills over MCP extension, discoverable with skills/list and readable at skill://<name>/<path> — add https://mcp.cloudflare.com/mcp to a compatible MCP client Markdown for Agents conversion limit raised to 6 MiB (from 2 MiB) of decompressed HTML; now uses an in-process streaming engine at the edge instead of buffering and forwarding to a separate service
+3 more
show less
Adds R2 bandwidth-by-Cloudflare-location chart in the Cloudflare UI, with per-bucket filtering and separate download vs. upload views; defaults to top five locations with a Top 5 locations dropdown supporting up to six at a time Reduces price of @cf/cloudflare/clef-flash to $0.038 per million input tokens (from $0.090); context window on hosted service reduced to 24K tokens (from 64K) — self-hosted weights on Hugging Face retain up to 256K context window Improves @cf/cloudflare/clef serving on Workers AI via SGLang, delivering up to 2x faster median decision latency (e.g., ~800-token inputs: 262 ms → 152 ms median; ~16K-token inputs: 2,721 ms → 1,635 ms median)
Adds cf.appsec.request.failed_detections field (type Array<String>) to Custom rules, Rate limiting rules, and Request Header Transform Rules — returns detection IDs for failures from content scanning, WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. PII PII Personally Identifiable Information — data that can identify a specific individual, such as names, email addresses, or SSNs. Cyber tools flag or redact it to limit exposure and meet privacy regulations. prompt injection prompt injection An attack where text the model reads, such as a web page, file or tool result, carries instructions that override the user's. It is the main security risk for agents with tools. Adds @cf/cloudflare/clef-omni to Workers AI — a 30B-parameter MoE MoE A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token. audio (WAV/MP3), videos (MP4/WebM), images, and text in a single request at $0.150 per million input tokens with a 64K context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. Cloudflare API MCP server now exposes Cloudflare skills via the Skills over MCP extension, discoverable with skills/list and readable at skill://<name>/<path> — add https://mcp.cloudflare.com/mcp to a compatible MCP client Adds R2 bandwidth-by-Cloudflare-location chart in the Cloudflare UI, with per-bucket filtering and separate download vs. upload views; defaults to top five locations with a Top 5 locations dropdown supporting up to six at a time
4 more in Everything
└──▷ BREAKING ON UPGRADE
! Converted Markdown for Agents responses no longer include the x-markdown-tokens or x-original-tokens response headers — clients that rely on these values must calculate token counts themselves.! Content-Length is removed from converted Markdown for Agents responses rather than recalculated, because the Markdown body is now streamed.! Passing an array directly to createBatch() in Cloudflare Workflows is deprecated (existing code continues to work, but the options-object form is now the supported API).! @cf/cloudflare/clef-flash hosted context window is reduced to 24K tokens (from 64K) — requests exceeding 24K input tokens will fail on the hosted service; switch to @cf/cloudflare/clef (64K) or self-host for larger contexts.
Cloudflare API v7.12.0 adds Nameserver Sets, Monetization rules, D1 undelete, Basin Catalog, K2 streams, Mesh nodes, and AI Search endpoints.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Restore an accidentally deleted D1 database before data is permanently gone.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/<account_id>/d1/database/<database_id>/undelete' \
-H 'Authorization: Bearer <CF_API_TOKEN>' \
-H 'Content-Type: application/json'
Adds Nameserver Sets CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. /accounts/{account_id}/dns_settings/nameserver_sets and /accounts/{account_id}/dns_settings/nameserver_sets/{nameserver_set_id} for managing custom nameserver sets per account.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Monetization API endpoints under /zones/{zone_id}/monetization/rules (and /{rule_id}) to list, deploy, update, get, and delete payment rules and rulesets. Adds POST /accounts/{account_id}/d1/database/{database_id}/undelete to restore a deleted D1 database. Adds Basin Catalog endpoints under /accounts/{account_id}/basin-catalog for listing, enabling, disabling, deleting metadata, managing credentials, namespaces, tables, and maintenance configs. Adds K2 streaming endpoints at /accounts/{account_id}/k2/streams (and /{stream_id}) and /accounts/{account_id}/k2/streams/{stream_id}/subscriptions for creating, reading, updating, and deleting K2 streams and their subscriptions.
+5 more
show less
Adds Mesh node management endpoints for listing, creating, updating, deleting nodes, retrieving tokens, managing connections and connectors, triggering manual failover, and configuring HA. Adds share lifecycle trigger endpoints for creating, renaming, deleting shares and managing recipients and resources within shares. Adds POST /accounts/{account_id}/workers/workers/{worker_id}/versions/{version_id}/profile to profile a specific Worker version. Adds PATCH /zones/{zone_id}/api_gateway/discovery/operations/{discovery_id} to edit a discovered web or API operation. Adds AI Search instance endpoints to create and update AI Search instances.
Adds Nameserver Sets CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. /accounts/{account_id}/dns_settings/nameserver_sets and /accounts/{account_id}/dns_settings/nameserver_sets/{nameserver_set_id} for managing custom nameserver sets per account.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Monetization API endpoints under /zones/{zone_id}/monetization/rules (and /{rule_id}) to list, deploy, update, get, and delete payment rules and rulesets. Adds POST /accounts/{account_id}/d1/database/{database_id}/undelete to restore a deleted D1 database. Adds Basin Catalog endpoints under /accounts/{account_id}/basin-catalog for listing, enabling, disabling, deleting metadata, managing credentials, namespaces, tables, and maintenance configs. Adds K2 streaming endpoints at /accounts/{account_id}/k2/streams (and /{stream_id}) and /accounts/{account_id}/k2/streams/{stream_id}/subscriptions for creating, reading, updating, and deleting K2 streams and their subscriptions.
+4 more
show less
Adds Mesh node management endpoints for listing, creating, updating, deleting nodes, retrieving tokens, managing connections and connectors, triggering manual failover, and configuring HA. Adds share lifecycle trigger endpoints for creating, renaming, deleting shares and managing recipients and resources within shares. Adds POST /accounts/{account_id}/workers/workers/{worker_id}/versions/{version_id}/profile to profile a specific Worker version. Adds AI Search instance endpoints to create and update AI Search instances.
1 more in Everything
Cloudflare adds MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats.
Adds failed detections field in Rules to control how rules handle requests based on reported detection failures.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Supports creating up to 100 Workflow instances at once by count or from a list via batch API, with per-instance error reporting in the result. Adds R2 bandwidth analytics broken down by the Cloudflare location that served each request. Cloudflare API MCP server now serves Cloudflare skills through the Skills over MCP extension. Markdown for Agents conversion switches to in-process streaming, supports larger HTML pages, and changes response headers.
Adds failed detections field in Rules to control how rules handle requests based on reported detection failures.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Supports creating up to 100 Workflow instances at once by count or from a list via batch API, with per-instance error reporting in the result. Adds R2 bandwidth analytics broken down by the Cloudflare location that served each request. Cloudflare API MCP server now serves Cloudflare skills through the Skills over MCP extension.
1 more in Everything
└──▷ BREAKING ON UPGRADE
! Markdown for Agents changes response headers — existing integrations that inspect those headers may need to be updated.
Cloudflare: Adds createBatch() to Cloudflare Workflows to create up to 100 Workflow instances in a single call with per-entry error reporting.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ USE IT
Trigger up to 100 Workflow instances in one API call when fanning out identical batch jobs (e.g. nightly reports) — avoids looping over individual create() calls.
javascript
copy
const { created, errors } = await env.MY_WORKFLOW.createBatch({ count: 50, params: { report: 'daily' } });
for (const error of errors) {
console.log(error.index, error.id, error.code, error.message);
}
Fan out per-order Workflow instances with individual IDs and params, catching any duplicates or quota errors in a single request.
javascript
copy
const { created, errors } = await env.MY_WORKFLOW.createBatch({
instances: [
{ id: 'order-1', params: { orderId: 1001 } },
{ id: 'order-2', params: { orderId: 1002 } },
],
});
for (const error of errors) {
console.log(error.index, error.id, error.code, error.message);
}
Updates the set of unsafe topic detection categories in AI Security for Apps; values available in cf.llm.prompt.unsafe_topic_categories have changed — existing WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
1 more in Everything
└──▷ BREAKING ON UPGRADE
! Values available in cf.llm.prompt.unsafe_topic_categories in AI Security for Apps have changed; WAF custom rules referencing a removed or renamed category will no longer match that category and must be updated to use the currently supported values.! The Log Explorer menu entry is no longer shown in the Cloudflare dashboard navigation; Log Explorer datasets are now accessed via Observability > Logs.! Passing an array directly to createBatch() in Cloudflare Workflows is deprecated; callers should migrate to the new options-object form with count or instances.
Cloudflare adds CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic. Rego Rego A declarative policy language created by the Open Policy Agent project, used to express authorization and compliance rules as code so cyber tools can evaluate structured data against those rules consistently. BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes. IPsec IPsec A suite of IETF protocols that authenticate and encrypt IP packets at the network layer, giving cyber tools a standards-based way to build VPNs or secure host-to-host tunnels without modifying applications. GRE GRE A tunneling protocol that wraps one network packet inside another, letting tools carry arbitrary traffic across IP networks without modifying the payload, useful for traffic capture and network emulation.
└──▷ HOW TO FIND IT
Create a CASB custom finding type to flag Google Workspace admin accounts missing two-factor authentication, using Rego logic evaluated against user assets.
📍 In Cloudflare One, go to Cloud & SaaS findings › Findings library › Create finding. Enter a name (e.g., Admin without 2FA ), description, and severity. Select provider Google Workspace and asset class users . Write your Rego expression (e.g., input.is_admin == true and input.two_factor_enabled == false) and select Validate, then select Create finding.
Adds an MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies. Supports routing non-RFC 1918 RFC 1918 IETF standard that reserves three IPv4 address ranges (10.x, 172.16–31.x, 192.168.x) for private networks, never routed on the public internet, giving tools a reliable way to identify internal traffic. Adds CASB custom finding types, letting security teams write detection logic in Rego (Open Policy Agent) scoped to a provider (e.g., Google Workspace, Microsoft 365) and asset class (users, files, groups) with built-in expression validation via Validate . Custom finding types work with CASB remediation policies to route matching findings to Slack, ServiceNow, or any webhook destination. BGP peering over IPsec and GRE tunnels is now generally available for Cloudflare WAN and Magic Transit production workloads.
+5 more
show less
Cloudflare Organizations is now generally available for Enterprise customers and MSSP MSSP A Managed Security Service Provider: a third-party company that operates cyber tooling and monitoring on behalf of clients, letting organizations outsource detection, response, and compliance functions. Adds a DNS records quota warning in the Cloudflare dashboard at 85% usage, reflecting either the zone-level or account-level quota. Moves Log Explorer datasets to the Observability > Logs page in the Cloudflare dashboard, combining Log Explorer and Workers Observability datasets under a shared filter builder, SQL editor, and visualizations. Adds a Windows service recovery mechanism backed by a scheduled task that starts the Cloudflare One Client service on system unlock if it is not already running (enabled by default). Improves connection reliability on Windows devices with very large hosts files by detecting them, allowing more time for the initial DNS check, and displaying a banner about longer connect times.
Adds an MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies. Supports routing non-RFC 1918 RFC 1918 IETF standard that reserves three IPv4 address ranges (10.x, 172.16–31.x, 192.168.x) for private networks, never routed on the public internet, giving tools a reliable way to identify internal traffic. Adds CASB custom finding types, letting security teams write detection logic in Rego (Open Policy Agent) scoped to a provider (e.g., Google Workspace, Microsoft 365) and asset class (users, files, groups) with built-in expression validation via Validate . Cloudflare Organizations is now generally available for Enterprise customers and MSSP MSSP A Managed Security Service Provider: a third-party company that operates cyber tooling and monitoring on behalf of clients, letting organizations outsource detection, response, and compliance functions. Adds a DNS records quota warning in the Cloudflare dashboard at 85% usage, reflecting either the zone-level or account-level quota.
+1 more
show less
Adds a Windows service recovery mechanism backed by a scheduled task that starts the Cloudflare One Client service on system unlock if it is not already running (enabled by default).
4 more in Everything
└──▷ BREAKING ON UPGRADE
! The Log Explorer menu item is no longer shown in the Cloudflare dashboard navigation; Log Explorer datasets are now accessed under Observability > Logs.
Cloudflare adds Log Explorer Observability integration, DNS quota warnings, Organizations GA, and consistent AI Gateway error responses.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ HOW TO FIND IT
Query your Log Explorer datasets after Log Search moves to Observability — navigate to the new location in the dashboard.
📍 In the Cloudflare dashboard, go to Logs › Observability, then select Log Explorer to query your datasets.
Adds Log Explorer dataset querying from the Observability Logs page in the Cloudflare dashboard (Log Search has moved to Logs > Observability).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds DNS records quota warnings on the DNS records page before the quota limit is reached. Standardizes provider authentication failure HTTP status codes through the AI Gateway REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Releases Cloudflare One Client version 2026.8.2100.0 for macOS, Windows, and Linux.
Adds Log Explorer dataset querying from the Observability Logs page in the Cloudflare dashboard (Log Search has moved to Logs > Observability).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds DNS records quota warnings on the DNS records page before the quota limit is reached.
2 more in Everything
└──▷ BREAKING ON UPGRADE
! Log Search has moved from its previous location to the Logs page under Observability in the Cloudflare dashboard — existing bookmarks or documentation pointing to the old location will no longer work.
└──▷ BREAKING ON UPGRADE
! Removed endpoint DELETE /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds/{curated_feed_id}! Removed endpoint GET /accounts/{account_id}/browser-rendering/devtools/browser! Removed endpoint GET /accounts/{account_id}/browser-rendering/devtools/browser/{session_id}! Removed endpoint GET /accounts/{account_id}/browser-rendering/devtools/browser/{session_id}/page/{target_id}! Removed endpoint GET /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs! Removed endpoint GET /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs/{job_id}! Removed endpoint PATCH /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds/{curated_feed_id}! Removed endpoint POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/skills/{skill_id}/diagnostic! Removed endpoint POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds! Removed endpoint POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds/bulk! Removed endpoint POST /accounts/{account_id}/hyperdrive/integrationsOperations/{integration}/createDatabaseSignature! Removed endpoint POST /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs! DELETE /accounts/{account_id}/r2/buckets/{bucket_name}/objects: response schema changed! POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/tags: response schema changed! POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/feeds: response schema changed! POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/skills: response schema changed! Deprecated endpoint GET /accounts/{account_id}/data-security/posture/policies/logs (still works)
Web Search API beta, strict service token auth, Pi Durable agent harness agent harness The software around an AI agent that manages its tools, execution loop, state and limits. It determines how the model's proposed actions are run and checked. hash_in_range() availability.
New integration Adds Web Search API (beta) at POST /{account_id}/ai/websearch/ supporting provider (ceramic, exa, linkup), limit, and options.gateway.id fields; routes through AI Gateway with Zero Data Retention and no markup over provider list price.Adds strict_service_token_auth field to PATCH https://api.cloudflare.com/client/v4/accounts/{account_id}/access/organizations to enforce consistent service-token-only auth — blocking redirects to login, ignoring Allow policies and CF_Authorization cookies, and logging failures in Access authentication logs. Adds --jurisdiction=us flag to wrangler d1 create for creating D1 databases that run and persist data within the United States. Adds --jurisdiction flag (values: eu, us, fedramp) to wrangler kv namespace create and cf kv namespaces create, and a jurisdiction field to POST /storage/kv/namespaces REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Adds PiHarness class to the Cloudflare Agents SDK (agents/harness/pi) for building durable long-running agents using the Pi Durable harness, with lifecycle persistence across restarts and crashes in Durable Objects.
+5 more
show less
Adds two new datasets — Workers Observability — Logs and Workers Observability — Traces (OTel) — to Custom Dashboards, enabling charts of Worker invocations, log levels, errors, CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware. Expands analytics retention to at least 31 days for Free and Pro domains across adaptive datasets (HTTP requests, security events, DNS analytics), with a 30-day single-query window; applies in the dashboard, Custom Dashboards, and the GraphQL Analytics API. Makes hash_in_range() globally available for HTTP products on all plans, enabling deterministic fractional traffic selection using fields like cf.random_seed. Raises the Custom Dashboards account limit to 100 dashboards. Consolidates domain analytics into a single tabbed view (Traffic, Performance, Security, Cache, Origin, DNS, Visitors) with a shared time range and filters; account-level analytics moved under Observability .
10 details in Everything
└──▷ BREAKING ON UPGRADE
! Zero Trust organizations created on or after October 5, 2026 have strict_service_token_auth enabled by default and cannot turn it off — service-token requests will never redirect to login and Allow policies will be ignored for those requests.
Cloudflare: New endpoint GET /accounts/{account_id}/argo/count_zones_enabled
└──▷ BREAKING ON UPGRADE
! Removed endpoint DELETE /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds/{curated_feed_id}! Removed endpoint GET /accounts/{account_id}/browser-rendering/devtools/browser! Removed endpoint GET /accounts/{account_id}/browser-rendering/devtools/browser/{session_id}! Removed endpoint GET /accounts/{account_id}/browser-rendering/devtools/browser/{session_id}/page/{target_id}! Removed endpoint GET /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs! Removed endpoint GET /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs/{job_id}! Removed endpoint PATCH /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds/{curated_feed_id}! Removed endpoint POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/skills/{skill_id}/diagnostic! Removed endpoint POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds! Removed endpoint POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds/bulk! Removed endpoint POST /accounts/{account_id}/hyperdrive/integrationsOperations/{integration}/createDatabaseSignature! Removed endpoint POST /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs! DELETE /accounts/{account_id}/r2/buckets/{bucket_name}/objects: response schema changed! POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/tags: response schema changed! POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/feeds: response schema changed! POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/skills: response schema changed! Deprecated endpoint GET /accounts/{account_id}/data-security/posture/policies/logs (still works)
Cloudflare adds Web Search API beta, strict service token auth, Pi Durable agent harness agent harness The software around an AI agent that manages its tools, execution loop, state and limits. It determines how the model's proposed actions are run and checked.
└──▷ TRY IT
Query the Web Search API from the CLI to ground an AI agent's response in live web results via AI Gateway.
copy
$ curl https://api.cloudflare.com/client/v4/accounts/$CLOUDFLARE_ACCOUNT_ID/ai/websearch/ \
-H 'Authorization: Bearer $CLOUDFLARE_API_TOKEN' \
-H 'Content-Type: application/json' \
--data '{"query": "latest CVEs in OpenSSL", "provider": "exa", "limit": 5, "options": {"gateway": {"id": "default"}}}' Create a Workers KV namespace locked to EU data residency to satisfy GDPR GDPR EU regulation enacted in 2018 that governs how organizations collect, store, and process personal data of EU residents, giving cyber tools legal obligations around data handling and breach notification.
copy
$ wrangler@latest kv namespace create NAMESPACE_NAME --jurisdiction=eu Enable strict service token authentication for an existing Zero Trust organization so that service-token requests are never redirected to login and Allow policies are bypassed.
copy
$ curl -X PATCH 'https://api.cloudflare.com/client/v4/accounts/{account_id}/access/organizations' \
-H 'Authorization: Bearer $CLOUDFLARE_API_TOKEN' \
-H 'Content-Type: application/json' \
--json '{"strict_service_token_auth": true}'
Adds strict_service_token_auth field to the PATCH https://api.cloudflare.com/client/v4/accounts/{account_id}/access/organizations endpoint to enforce consistent service-token-only authentication behavior in Cloudflare Access.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds hash_in_range() function to Cloudflare Rules expressions across all plans and HTTP products, enabling deterministic percentage-based request sampling using cf.random_seed. Introduces Web Search API (beta) at /{account_id}/ai/websearch/ supporting query, provider (ceramic, exa, linkup), limit, and options.gateway.id parameters, routing search through AI Gateway with Zero Data Retention. Adds PiHarness class to the Cloudflare Agents SDK (agents/harness/pi) for building durable long-running AI agents using the Pi 1.0 / Pi Durable harness, with support for tools, extensions, and lifecycle persistence in Durable Objects. Enables strict service token authentication by default for Zero Trust organizations created on or after October 5, 2026, enforcing service-token-only policies and suppressing login redirects and CF_Authorization cookie issuance on authenticated requests.
5 details in Everything
└──▷ BREAKING ON UPGRADE
! Zero Trust organizations created on or after October 5, 2026 have strict_service_token_auth enabled by default and cannot disable it — requests with service token headers will never be redirected to the login page, Allow policies are ignored, and no CF_Authorization cookie is returned.
API surface changed: +33 endpoints, −12 endpoints, 71 modified, 1 deprecated︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
New endpoint DELETE /accounts/{account_id}/access/user_populations/{user_population_id}︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New endpoint DELETE /accounts/{account_id}/access/users/{user_id}/passkeys/{authenticator_id} New endpoint DELETE /accounts/{account_id}/k2/streams/{stream_id} New endpoint DELETE /zones/{zone_id}/monetization/rules New endpoint DELETE /zones/{zone_id}/monetization/rules/{rule_id}
+38 more
show less
New endpoint GET /accounts/{account_id}/access/user_populations New endpoint GET /accounts/{account_id}/access/user_populations/{user_population_id} New endpoint GET /accounts/{account_id}/ai-gateway/gateways/{gateway_id}/provider_configs/{id} New endpoint GET /accounts/{account_id}/basin-catalog/{bucket_name}/credential/status New endpoint GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/search New endpoint GET /accounts/{account_id}/k2/streams New endpoint GET /accounts/{account_id}/k2/streams/{stream_id} New endpoint GET /accounts/{account_id}/k2/streams/{stream_id}/subscriptions New endpoint GET /accounts/{account_id}/monetization New endpoint GET /accounts/{account_id}/r2-catalog/{bucket_name}/credential/status New endpoint GET /accounts/{account_tag}/analytics/sql New endpoint GET /accounts/{account_tag}/analytics/sql/introspection New endpoint GET /zones/{zone_id}/monetization New endpoint GET /zones/{zone_id}/monetization/rules New endpoint GET /zones/{zone_id}/monetization/rules/{rule_id} New endpoint PATCH /accounts/{account_id}/k2/streams/{stream_id} New endpoint PATCH /accounts/{account_id}/workers/dispatch/namespaces/{dispatch_namespace}/scripts/{script_name}/tags/{tag} New endpoint PATCH /zones/{zone_id}/monetization/rules/{rule_id} New endpoint POST /accounts/{account_id}/access/user_populations New endpoint POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/skills/{skill_id}/run New endpoint POST /accounts/{account_id}/hyperdrive/integrationsOperations/planetScale/createDatabaseSignature New endpoint POST /accounts/{account_id}/k2/streams New endpoint POST /accounts/{account_id}/monetization New endpoint POST /accounts/{account_id}/r2/buckets/{bucket_name}/jobs New endpoint POST /accounts/{account_tag}/analytics/sql New endpoint POST /zones/{zone_id}/monetization New endpoint PUT /accounts/{account_id}/access/user_populations/{user_population_id} New endpoint PUT /zones/{zone_id}/monetization/rules GET /accounts/{account_id}/cloudforce-one/events: param searchBranches (query) added POST /accounts/{account_id}/browser-rendering/accessibilityTree: param browser (query) added POST /accounts/{account_id}/browser-rendering/content: param browser (query) added POST /accounts/{account_id}/browser-rendering/json: param browser (query) added POST /accounts/{account_id}/browser-rendering/links: param browser (query) added POST /accounts/{account_id}/browser-rendering/markdown: param browser (query) added POST /accounts/{account_id}/browser-rendering/pdf: param browser (query) added POST /accounts/{account_id}/browser-rendering/scrape: param browser (query) added POST /accounts/{account_id}/browser-rendering/screenshot: param browser (query) added POST /accounts/{account_id}/browser-rendering/snapshot: param browser (query) added
43 details in Everything
└──▷ BREAKING ON UPGRADE
! Removed endpoint DELETE /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds/{curated_feed_id}! Removed endpoint GET /accounts/{account_id}/browser-rendering/devtools/browser! Removed endpoint GET /accounts/{account_id}/browser-rendering/devtools/browser/{session_id}! Removed endpoint GET /accounts/{account_id}/browser-rendering/devtools/browser/{session_id}/page/{target_id}! Removed endpoint GET /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs! Removed endpoint GET /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs/{job_id}! Removed endpoint PATCH /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds/{curated_feed_id}! Removed endpoint POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/skills/{skill_id}/diagnostic! Removed endpoint POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds! Removed endpoint POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/curated-feeds/bulk! Removed endpoint POST /accounts/{account_id}/hyperdrive/integrationsOperations/{integration}/createDatabaseSignature! Removed endpoint POST /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs! DELETE /accounts/{account_id}/r2/buckets/{bucket_name}/objects: response schema changed! POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/tags: response schema changed! POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/feeds: response schema changed! POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/skills: response schema changed! Deprecated endpoint GET /accounts/{account_id}/data-security/posture/policies/logs (still works)
Cloudflare launches Web Search API in open beta, letting AI agents query the web via REST or Workers AI binding through AI Gateway.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds the provider parameter to select between Ceramic.ai, Exa, and Linkup search providers, with all providers returning results in the same structured format (titles, URLs, descriptions).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New Cloudflare Web Search API lets AI agents and applications issue a search query and receive structured web results (titles, URLs, descriptions) via REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Routes Web Search API calls through AI Gateway, giving every search request the same logging, analytics, billing, and access controls as model inference requests. Supports Unified Billing so searches are charged to AI Gateway credits at each provider's list API price with no markup, or with a bring-your-own provider API key option.
4 details in Everything
Cloudflare: Adds Web Search API (beta) at POST /accounts/{account_id}/ai/websearch/, letting AI agents query live Internet results through three providers — ceramic, exa, and linkup — with query, provider, limit, and options.gateway.id parameters; also callable from a Worker via env.AI.websearch() .︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Ground an AI agent's response in live search results from Exa, routed through AI Gateway for logging and billing.
copy
$ curl https://api.cloudflare.com/client/v4/accounts/$CLOUDFLARE_ACCOUNT_ID/ai/websearch/ \
-H 'Authorization: Bearer $CLOUDFLARE_API_TOKEN' \
-H 'Content-Type: application/json' \
-d '{"query": "latest CVEs in OpenSSL", "provider": "exa", "limit": 5, "options": {"gateway": {"id": "default"}}}' Share a local webhook receiver with a specific colleague over a Quick Tunnel without exposing it to the public internet.
copy
$ cloudflared tunnel --url http://localhost:8080 --allowed-mail 'alice@example.com,bob@example.com' Create a Workers KV namespace pinned to EU storage to meet GDPR GDPR EU regulation enacted in 2018 that governs how organizations collect, store, and process personal data of EU residents, giving cyber tools legal obligations around data handling and breach notification.
copy
$ wrangler kv namespace create MY_NAMESPACE --jurisdiction eu
Adds --jurisdiction flag to wrangler kv namespace create and the POST /accounts/{account_id}/storage/kv/namespaces REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. eu, us, and fedramp; now generally available. Adds two new datasets — Workers Observability — Logs and Workers Observability — Traces (OTel OTel An open standard and set of tools for collecting traces, metrics and logs from applications. It lets services export observability data without tying instrumentation to one monitoring vendor. CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware. Raises Custom Dashboards per-account limit to 100 dashboards. Extends analytics data retention to at least 31 days for Free and Pro domains across adaptive datasets (HTTP requests, security events, DNS analytics), with a 30-day single-request query window, up from as little as 24 hours. Consolidates domain analytics into a single Analytics section in the Cloudflare dashboard with Traffic, Performance, Security, Cache, Origin, DNS, and Visitors tabs sharing one time range and filter set.
+1 more
show less
Releases @cloudflare/workers-oauth-provider v1 with a split OAuthAuthorizationServer / OAuthResourceServer API supporting MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Client ID Metadata Documents Client ID Metadata Documents OAuth 2.0 documents hosted at a client's own URL that declare its identity and redirect URIs, letting authorization servers fetch and verify client metadata without manual registration. insufficientScope() for step-up authorization, and multi-MCP-server MCP-server A process that exposes tools, resources, and prompts over Anthropic's Model Context Protocol, letting an AI agent call external APIs or local services through a standardised interface.
Adds two new datasets — Workers Observability — Logs and Workers Observability — Traces (OTel OTel An open standard and set of tools for collecting traces, metrics and logs from applications. It lets services export observability data without tying instrumentation to one monitoring vendor. CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware.
5 more in Everything
Cloudflare: Introduces Web Search API to ground AI agents and applications with real-time web search results.
Adds Cloudflare Observability as a unified documentation and product surface covering logs, traces, analytics, alerts, telemetry export, and dashboards.
1 detail in Everything
Cloudflare: Adds Workers KV namespace jurisdictions (EU, US, FedRAMP FedRAMP A US government program that standardizes cloud security authorization, letting vendors get a single assessment accepted across federal agencies instead of repeating the process for each one.
└──▷ TRY IT
Lock down a Quick Tunnel so only teammates with a specific corporate email domain can access it — useful for sharing internal previews without a full Access policy.
copy
$ cloudflared tunnel --url http://localhost:8080 --allowed-mail @yourcompany.com
Introduces Web Search API through AI Gateway, enabling AI agents and applications to search the web via Ceramic.ai, Exa, and Linkup. Extends adaptive analytics dataset retention to at least 31 days on all plans, including Free and Pro, covering HTTP, security, and DNS analytics. Custom Dashboards can now chart Workers Observability logs and traces alongside analytics and Log Explorer data. Introduces Clef and Clef-flash, Cloudflare's first open-source decision models on Workers AI, licensed under Apache 2.0, returning typed answers with probabilities.
Introduces Web Search API through AI Gateway, enabling AI agents and applications to search the web via Ceramic.ai, Exa, and Linkup. Introduces Clef and Clef-flash, Cloudflare's first open-source decision models on Workers AI, licensed under Apache 2.0, returning typed answers with probabilities.
2 more in Everything
└──▷ TRY IT
Lock a Quick Tunnel to only allow specific email addresses — useful for sharing a local dev service with teammates without a full Access policy.
copy
$ cloudflared tunnel --url http://localhost:8080 --allowed-mail alice@example.com --allowed-mail bob@example.com
Cloudflare K2 launches as a durable log service with configurable retention, Workers bindings, and HTTP API production︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds Workers binding support to produce records to a K2 stream directly from a Worker.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds HTTP API support to produce records to a K2 stream over HTTP. Introduces K2 streams — a new durable log service on Workers Paid plan that decouples event producers and consumers with configurable retention up to 30 days (longer available by request). Supports subscriptions to share records across a group of consumers or deliver every record to multiple independent consumers independently.
4 details in Everything
Cloudflare AI Search gains hybrid search hybrid search Combining keyword search with semantic or vector search. The results use both exact term matches and similarity in meaning. multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. embeddings embeddings Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. OCR OCR Optical character recognition, converting text in an image or scanned document into machine-readable characters. It lets software search or process text that was stored as pixels.
Enables hybrid search combining semantic and keyword matching in the same query, active by default.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds image search using a multimodal embedding model embedding model Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. Adds optical character recognition optical character recognition Optical character recognition, converting text in an image or scanned document into machine-readable characters. It lets software search or process text that was stored as pixels.
3 details in Everything
Cloudflare Workers AI gains two proprietary multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. clef, clef-flash) that return per-option probabilities from text, JSON, image, or video state.
New supported platform Adds clef (27B multimodal decision model) to Workers AI, accepting text, JSON, images, or video as state input and returning probabilities for typed question schemas.New supported platform Adds clef-flash (9B multimodal decision model) to Workers AI as a faster variant of Clef, accepting text, JSON, images, or video and returning per-option probabilities.
2 details in Everything
Cloudflare adds --allowed-mail Quick Tunnel auth, Clef/Clef-flash decision models on Workers AI, OAuth Provider v1 split API, and AI Search GA︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Share a local webhook receiver or demo with specific colleagues over a Quick Tunnel without exposing it to everyone who has the URL.
copy
$ cloudflared tunnel --url http://localhost:8080 --allowed-mail 'alice@example.com,bob@example.com' Route a support ticket to the right team in milliseconds using a Clef decision model directly in the Workers request path.
javascript
copy
const response = await env.AI.run('@cf/cloudflare/clef', {
model: 'clef',
state: 'Checkout has been failing for every customer for the last hour.',
questions: {
urgent: { type: 'noul', instructions: 'Is this support request urgent?' },
team: {
type: 'choice',
instructions: 'Which team should handle this request?',
criteria: {
billing: 'Payments, invoices, and refunds',
technical: 'Outages, errors, and configuration',
sales: 'Plans and upgrades'
}
}
}
});
// response.answers.urgent.noul -> probability the request is urgent
// response.answers.team.choice -> highest-probability team
Wire a calendar MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
wrangler.toml
copy
# wrangler.toml for the calendar-mcp Worker
name = "calendar-mcp"
main = "src/index.ts"
compatibility_date = "2026-10-02"
[[services]]
binding = "AUTH_SERVER"
service = "auth-server"
entrypoint = "AuthServer"
Adds --allowed-mail flag to cloudflared tunnel --url to restrict Quick Tunnel access to specific email addresses (single address, comma-separated list, or wildcard domain like *@example.com) via one-time PIN authentication — no Cloudflare account required for visitors.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Introduces @cf/cloudflare/clef (27B, 64K context) and @cf/cloudflare/clef-flash (9B, 64K context) open-source decision models on Workers AI, returning structured probability answers (noul, choice, score question types) instead of free-form text — callable via env.AI.run() or the /ai/run REST endpoint. Releases @cloudflare/workers-oauth-provider v1 with a split OAuthAuthorizationServer / OAuthResourceServer API: the authorization server issues tokens for multiple MCP servers, the resource server validates them over a Service Binding (AUTH_SERVER.validateToken) without a public-Internet round trip, and insufficientScope() enables step-up authorization in one call. Adds refreshTokenIdleTTL config key to @cloudflare/workers-oauth-provider for sliding refresh-token expiry. Adds purgeExpiredData() method to @cloudflare/workers-oauth-provider for resumable KV cleanup.
+4 more
show less
Supports clientIdMetadataDocumentEnabled: true in OAuthAuthorizationServer to enable Client ID Metadata Documents Client ID Metadata Documents OAuth 2.0 documents hosted at a client's own URL that declare its identity and redirect URIs, letting authorization servers fetch and verify client metadata without manual registration. AI Search is now generally available with hybrid search hybrid search Combining keyword search with semantic or vector search. The results use both exact term matches and similarity in meaning. embedding embedding Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. reranking reranking A model that re-scores a first batch of search results against the query and reorders them, more accurately than the fast first-stage search. Launches a reinforcement learning fine-tuning service for Clef models to tune decision models on custom workloads. Ships a migration skill at node_modules/@cloudflare/workers-oauth-provider/skills/migrate-to-1.0/SKILL.md so a coding agent can upgrade from @cloudflare/workers-oauth-provider 0.x to v1.
Adds --allowed-mail flag to cloudflared tunnel --url to restrict Quick Tunnel access to specific email addresses (single address, comma-separated list, or wildcard domain like *@example.com) via one-time PIN authentication — no Cloudflare account required for visitors.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Introduces @cf/cloudflare/clef (27B, 64K context) and @cf/cloudflare/clef-flash (9B, 64K context) open-source decision models on Workers AI, returning structured probability answers (noul, choice, score question types) instead of free-form text — callable via env.AI.run() or the /ai/run REST endpoint. Adds refreshTokenIdleTTL config key to @cloudflare/workers-oauth-provider for sliding refresh-token expiry. Adds purgeExpiredData() method to @cloudflare/workers-oauth-provider for resumable KV cleanup. Supports clientIdMetadataDocumentEnabled: true in OAuthAuthorizationServer to enable Client ID Metadata Documents Client ID Metadata Documents OAuth 2.0 documents hosted at a client's own URL that declare its identity and redirect URIs, letting authorization servers fetch and verify client metadata without manual registration.
+2 more
show less
Launches a reinforcement learning fine-tuning service for Clef models to tune decision models on custom workloads. Ships a migration skill at node_modules/@cloudflare/workers-oauth-provider/skills/migrate-to-1.0/SKILL.md so a coding agent can upgrade from @cloudflare/workers-oauth-provider 0.x to v1.
2 more in Everything
Cloudflare API v7.12.0 adds Nameserver Sets, Basin Catalog, and Mesh node management endpoints︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Enable a Basin Catalog bucket so it is available for query and data-sharing workflows.
copy
$ curl -s -X POST 'https://api.cloudflare.com/client/v4/accounts/<account_id>/basin-catalog/<bucket_name>/enable' \
-H 'Authorization: Bearer <token>'
Adds GET/POST /accounts/{account_id}/dns_settings/nameserver_sets and GET/DELETE /accounts/{account_id}/dns_settings/nameserver_sets/{nameserver_set_id} endpoints to list, create, retrieve, and delete Custom Nameserver Sets.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Basin Catalog endpoints under /accounts/{account_id}/basin-catalog to list, retrieve, enable, disable, delete metadata, manage maintenance configs, credentials, namespaces, tables, and table-level maintenance configs for catalog buckets. Adds Mesh node management endpoints to list, get, create, update, delete, and retrieve tokens for Mesh nodes, plus connection listing, connector retrieval, manual failover triggering, and HA configuration get/update. Adds Mesh share lifecycle endpoints to trigger share creation, rename, deletion, recipient addition/removal, and resource addition, metadata update, and deletion. Updates the cloudflare-go SDK to v7.12.0, installable via go get -u github.com/cloudflare/cloudflare-go/v7@v7.12.0.
Adds GET/POST /accounts/{account_id}/dns_settings/nameserver_sets and GET/DELETE /accounts/{account_id}/dns_settings/nameserver_sets/{nameserver_set_id} endpoints to list, create, retrieve, and delete Custom Nameserver Sets.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Basin Catalog endpoints under /accounts/{account_id}/basin-catalog to list, retrieve, enable, disable, delete metadata, manage maintenance configs, credentials, namespaces, tables, and table-level maintenance configs for catalog buckets. Adds Mesh node management endpoints to list, get, create, update, delete, and retrieve tokens for Mesh nodes, plus connection listing, connector retrieval, manual failover triggering, and HA configuration get/update. Adds Mesh share lifecycle endpoints to trigger share creation, rename, deletion, recipient addition/removal, and resource addition, metadata update, and deletion.
1 more in Everything
Cloudflare adds Basin analytics platform, K2 durable event stream, and Monetization Gateway to its product directory.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Cloudflare: Introduces Clef and Clef-flash , Cloudflare's first open-source (Apache 2.0) decision models on Workers AI, returning typed answers with probabilities — leading 7 of 10 decision benchmarks and running up to 13x faster than Jev.
└──▷ TRY IT
Lock a Quick Tunnel to a specific email domain so only your org's users can reach it — useful for exposing a local dev service during testing.
copy
$ cloudflared tunnel --url http://localhost:8080 --allowed-mail @example.com
Workers OAuth Provider reaches v1 with a split API separating the authorization server from MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. AI Search is now generally available with usage-based pricing, included Workers AI calls, and new search, model, file, and configuration capabilities. Artifacts enters open beta with Workers Builds integration, programmable repository workflows, event subscriptions, data localization, and metrics. Cloudflare One now requires only the Zero Trust Write API token permission to tag targets with Access for Infrastructure.
Artifacts enters open beta with Workers Builds integration, programmable repository workflows, event subscriptions, data localization, and metrics.
3 more in Everything
30 days of analytics data on every plan
Oct 2, 2026
· release notes
All plans now receive 30 days of retained analytics data with unified domain analytics views in the dashboard and GraphQL API.
Increases minimum retention for adaptive analytics datasets (HTTP requests, security events, DNS) to at least 31 days on Free and Pro domains Expands allowed query window to 30 days in a single request for adaptive analytics datasets Unifies domain analytics view in the dashboard with Traffic, Performance, Security, Cache, Origin, DNS, and Visitors tabs sharing one time range and filters Places account-level analytics under Observability > Analytics
4 details in Everything
Wrangler now supports D1 databases with --jurisdiction=us for US data residency.
└──▷ USE IT
Provision a new D1 database that strictly persists data within the United States for compliance.
shell
copy
npx wrangler@latest d1 create db-with-us-jurisdiction --jurisdiction=us
Adds --jurisdiction=us argument to wrangler d1 create to provision databases within United States jurisdiction Enables creation of D1 databases constrained to US-only data persistence and processing
2 details in Everything
Run the Pi Durable harness on Cloudflare with the Agents SDK
Oct 2, 2026
· release notes
Cloudflare Agents SDK adds PiHarness class for durable long-running agents via first-class Pi harness support
Introduces the new PiHarness class in the Cloudflare Agents SDK to build long-running agents that persist state durably across restarts and crashes Adds agents/models/pi-ai entry point to connect PiHarness with Cloudflare Workers AI or external Pi AI providers Enables tool registration via registry.install() within the PiHarness harness factory before calling Harness.open()
3 details in Everything
hash_in_range() is globally available for HTTP products
Oct 2, 2026
· release notes
hash_in_range() function now globally available for all HTTP products on all plans
Enables request sampling and controlled rollouts using the new hash_in_range() function in WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
1 detail in Everything
Cloudflare introduces Web Search API in beta for grounding AI responses in live web data via AI Gateway
New POST /client/v4/accounts/:accountId/ai/websearch/ REST endpoint enables internet search for AI applications with Zero Data Retention. New env.AI.websearch() method available in Cloudflare Workers for programmatic web search integration. Support for Ceramic.ai, Exa, and Linkup as initial search providers through the Web Search API.
3 details in Everything
Workers KV namespace jurisdictions are now generally available
Oct 2, 2026
· release notes
Workers KV now supports jurisdictions (eu, us, fedramp) for data localization
Adds jurisdiction argument to wrangler kv namespace create to set durable storage region at creation time Adds --jurisdiction flag to cf kv namespaces create to enforce data residency during namespace provisioning Extends the POST /client/v4/accounts/{account_id}/storage/kv/namespaces API endpoint with a jurisdiction request body field
3 details in Everything
Workers Observability logs and traces in Custom Dashboards
Oct 2, 2026
· release notes
Adds Workers Observability — Logs and Traces (OTel OTel An open standard and set of tools for collecting traces, metrics and logs from applications. It lets services export observability data without tying instrumentation to one monitoring vendor.
Workers Observability — Logs and Workers Observability — Traces (OTel) datasets let you chart Worker invocations, log levels, errors, CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware. Custom Dashboards now allow up to 100 dashboards for every account
2 details in Everything
Protect Quick Tunnels with email authentication
Oct 2, 2026
· release notes
Cloudflare Tunnel adds --allowed-mail flag to restrict Quick Tunnel access via email authentication
Adds the --allowed-mail flag to cloudflared tunnel to require one-time PIN verification for visitors Supports single emails, comma-separated lists ('alice@example.com,bob@example.com'), and domain wildcards (*@example.com) in --allowed-mail
2 details in Everything
Cloudflare Basin Catalog brings a managed Apache Iceberg REST catalog Apache Iceberg REST catalog A standard HTTP API specification for querying and managing an Iceberg table catalog, letting cyber tools from different vendors discover, read, and write Iceberg metadata without vendor-specific integrations.
Adds Basin Catalog, a managed Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS. Turns an R2 bucket into a data warehouse or lakehouse for log analytics, business intelligence, and data pipeline workloads with R2's zero-egress fee model.
2 details in Everything
Cloudflare Basin Pipelines: ingest streaming data via HTTP or Worker bindings, transform with SQL, and deliver to R2 as Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS. Parquet Parquet A columnar storage file format maintained by the Apache Software Foundation, designed for efficient compression and fast analytical queries, making it a common choice for storing and processing large structured datasets.
└──▷ TRY IT
Bootstrap your first Basin Pipeline — sets up a stream, pipeline, and R2 sink in one step.
copy
$ npx wrangler basin pipelines setup
Adds wrangler basin pipelines setup CLI command to scaffold a new Basin Pipeline from the terminal.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Introduces Basin Pipelines, a new managed streaming ETL service that ingests events via HTTP endpoints or Worker bindings, applies SQL-based transformations, and delivers exactly-once to R2 as Apache Iceberg tables or Parquet and JSON files. Adds Streams — durable, buffered queues that receive events via HTTP endpoints or Worker bindings. Adds Pipelines — connects streams to sinks with SQL transformations that validate, filter, transform, and enrich data at ingestion time. Adds Sinks — configurable destinations that write Apache Iceberg tables to Basin Catalog or export as Parquet and JSON files in R2.
+1 more
show less
Supports fan-out patterns, enabling a single stream to be routed into multiple Iceberg tables.
6 details in Everything
Cloudflare Basin GA: serverless analytics platform with Pipelines ingestion, Iceberg Catalog Iceberg Catalog An open REST API specification, maintained by the Apache Iceberg community, that lets compute engines discover and manage Iceberg table metadata without vendor lock-in.
└──▷ TRY IT
Bootstrap a full event-ingestion pipeline — stream, sink, and pipeline in one step — to start writing analytics events to R2 Iceberg tables.
copy
$ npx wrangler basin pipelines setup Enable the Iceberg REST catalog on an existing R2 bucket so external engines (Spark, Trino, etc.) can register and query tables stored there.
copy
$ npx wrangler basin catalog enable YOUR_BUCKET_NAME Run a quick ad-hoc OLAP query against a Basin-managed Iceberg table without spinning up a query cluster.
copy
$ npx wrangler basin sql query YOUR_WAREHOUSE_NAME "SELECT * FROM default.events LIMIT 10"
Adds wrangler basin pipelines setup command to configure a stream, sink, and pipeline for HTTP or Workers-binding-based event ingestion with SQL transformations writing to R2 Iceberg tables.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds wrangler basin catalog enable <bucket> command to enable the Iceberg REST catalog and automatic table maintenance on an existing R2 bucket. Adds wrangler basin sql query <warehouse> <sql> command to run distributed OLAP queries across catalog tables on Cloudflare's global network without managing query clusters. Basin Pipelines ingestion limit raised from 5 MB/s to 1 GB/s per stream. R2 Data Catalog adds table maintenance schedule visibility, run history, and manual compaction queueing from the dashboard.
+3 more
show less
R2 Data Catalog now supports read-only API tokens for connecting external query engines. R2 Data Catalog compaction now automatically rewrites and clusters Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS. Cloudflare Basin is now generally available, unifying ingestion (Basin Pipelines), Iceberg table management (Basin Catalog), and SQL analytics (Basin SQL) on R2.
Adds wrangler basin pipelines setup command to configure a stream, sink, and pipeline for HTTP or Workers-binding-based event ingestion with SQL transformations writing to R2 Iceberg tables.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds wrangler basin catalog enable <bucket> command to enable the Iceberg REST catalog and automatic table maintenance on an existing R2 bucket. Adds wrangler basin sql query <warehouse> <sql> command to run distributed OLAP queries across catalog tables on Cloudflare's global network without managing query clusters. Cloudflare Basin is now generally available, unifying ingestion (Basin Pipelines), Iceberg table management (Basin Catalog), and SQL analytics (Basin SQL) on R2.
4 more in Everything
Cloudflare GA's Basin analytics platform, adds ML-KEM ML-KEM NIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake. ML-DSA ML-DSA NIST's main post-quantum digital signature standard (FIPS 204), formerly Dilithium. It is the planned replacement for RSA and ECDSA signatures on certificates and code. post-quantum post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA. x402 x402 A proposed HTTP payment protocol revival using status code 402, enabling machine-to-machine micropayments over HTTP so cyber tools can gate API access or resources behind automated, per-request cryptocurrency payments.
└──▷ USE IT
Enable post-quantum key encapsulation in a Workers project so ML-KEM-768 ML-KEM-768 NIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake.
wrangler.toml
copy
compatibility_flags = ["webcrypto_modern_algorithms"]
Bootstrap a full Basin end-to-end data pipeline from the CLI in one step.
copy
$ wrangler basin pipelines setup Pay for an AI inference request directly from a stablecoin wallet via the x402 protocol instead of using a prepaid credit balance.
copy
$ curl -iX POST "https://api.cloudflare.com/client/v4/accounts/$CLOUDFLARE_ACCOUNT_ID/ai/run" -H "Authorization: Bearer $CLOUDFLARE_API_TOKEN" -H "Payment-Method: x402" -H "Content-Type: application/json" -d '{"model": "z-ai/glm-4.7-flash", "input": {"messages": [{"role": "user", "content": "What is Cloudflare?"}]}}'
Enables the webcrypto_modern_algorithms compatibility flag to unlock ML-KEM-768, ML-KEM-1024 ML-KEM-1024 NIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake. ML-DSA-65 ML-DSA-65 NIST's main post-quantum digital signature standard (FIPS 204), formerly Dilithium. It is the planned replacement for RSA and ECDSA signatures on certificates and code. ML-DSA-87 ML-DSA-87 NIST's main post-quantum digital signature standard (FIPS 204), formerly Dilithium. It is the planned replacement for RSA and ECDSA signatures on certificates and code. encapsulateBits, decapsulateBits, getPublicKey() , SubtleCrypto.supports() , and JSON Web Keys with the AKP key type.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds durable_object_io_tasks_prevent_eviction compatibility flag (default on 2026-10-01+) so Durable Objects stay alive — up to 15 minutes per pending operation — while awaiting service binding responses, RPC RPC Remote Procedure Call, a protocol that lets a program execute a function on another machine as if it were local, giving cyber tools a structured way to communicate across processes or hosts without managing raw sockets. fetch() calls to other Durable Objects, this.ctx.container.monitor() , this.ctx.waitUntil() promises, and setTimeout() /setInterval() timers, even without a connected client. Launches Basin generally available — an end-to-end analytics platform comprising Basin Pipelines (formerly Cloudflare Pipelines), Basin Catalog (formerly R2 Data Catalog), and Basin SQL (formerly R2 SQL), bootstrapped with wrangler basin pipelines setup. Basin Pipelines now ingests up to 1 GB/s per stream, up from 5 MB/s, enabling high-volume event, telemetry, and log ingestion without splitting across streams. Basin Pipelines supports filtering and reshaping Cloudflare logs before storing them as Iceberg tables, Parquet, or JSON, with typed Workers bindings and a dashboard for investigating dropped events.
+5 more
show less
Basin Catalog manages Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS. Basin SQL provides a serverless distributed SQL engine for Apache Iceberg tables in Basin Catalog, supporting window functions, grouping sets, approximate aggregates, joins, CTEs, set operations, EXPLAIN, and more than 190 built-in functions. Releases Sandbox SDK 1.0 with a Durable Object container API on this.ctx.container, enabling per-sandbox image and instance-size selection, container snapshots (public beta), exec() with streamed I/O, terminal support, preview serving from sandbox ports, and the @cloudflare/sandbox package with Files , S3Mount , and DirectoryBackup helper classes. AI Gateway adds Machine Payments (beta) via the x402 protocol: authenticate with a Cloudflare API token and send Payment-Method: x402 to the /ai/run endpoint so stablecoin-wallet clients pay for inference directly without a prepaid credit balance. Browser Isolation policies gain RBAC RBAC Role-based access control, where permissions are assigned to roles such as reader or administrator and users receive those roles. It makes access easier to manage than individual permission lists. Zero Trust HTTP Policies Admin account-level role or a resource-scoped role to control access to specific isolation policies, including policy settings for copy/paste, file download/upload, keyboard, and printing.
Enables the webcrypto_modern_algorithms compatibility flag to unlock ML-KEM-768, ML-KEM-1024 ML-KEM-1024 NIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake. ML-DSA-65 ML-DSA-65 NIST's main post-quantum digital signature standard (FIPS 204), formerly Dilithium. It is the planned replacement for RSA and ECDSA signatures on certificates and code. ML-DSA-87 ML-DSA-87 NIST's main post-quantum digital signature standard (FIPS 204), formerly Dilithium. It is the planned replacement for RSA and ECDSA signatures on certificates and code. encapsulateBits, decapsulateBits, getPublicKey() , SubtleCrypto.supports() , and JSON Web Keys with the AKP key type.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds durable_object_io_tasks_prevent_eviction compatibility flag (default on 2026-10-01+) so Durable Objects stay alive — up to 15 minutes per pending operation — while awaiting service binding responses, RPC RPC Remote Procedure Call, a protocol that lets a program execute a function on another machine as if it were local, giving cyber tools a structured way to communicate across processes or hosts without managing raw sockets. fetch() calls to other Durable Objects, this.ctx.container.monitor() , this.ctx.waitUntil() promises, and setTimeout() /setInterval() timers, even without a connected client. Launches Basin generally available — an end-to-end analytics platform comprising Basin Pipelines (formerly Cloudflare Pipelines), Basin Catalog (formerly R2 Data Catalog), and Basin SQL (formerly R2 SQL), bootstrapped with wrangler basin pipelines setup. Basin Pipelines supports filtering and reshaping Cloudflare logs before storing them as Iceberg tables, Parquet, or JSON, with typed Workers bindings and a dashboard for investigating dropped events. Basin Catalog manages Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS.
+4 more
show less
Basin SQL provides a serverless distributed SQL engine for Apache Iceberg tables in Basin Catalog, supporting window functions, grouping sets, approximate aggregates, joins, CTEs, set operations, EXPLAIN, and more than 190 built-in functions. Releases Sandbox SDK 1.0 with a Durable Object container API on this.ctx.container, enabling per-sandbox image and instance-size selection, container snapshots (public beta), exec() with streamed I/O, terminal support, preview serving from sandbox ports, and the @cloudflare/sandbox package with Files , S3Mount , and DirectoryBackup helper classes. AI Gateway adds Machine Payments (beta) via the x402 protocol: authenticate with a Cloudflare API token and send Payment-Method: x402 to the /ai/run endpoint so stablecoin-wallet clients pay for inference directly without a prepaid credit balance. Browser Isolation policies gain RBAC RBAC Role-based access control, where permissions are assigned to roles such as reader or administrator and users receive those roles. It makes access easier to manage than individual permission lists. Zero Trust HTTP Policies Admin account-level role or a resource-scoped role to control access to specific isolation policies, including policy settings for copy/paste, file download/upload, keyboard, and printing.
1 more in Everything
Cloudflare adds Basin Catalog API endpoints for managing data buckets, namespaces, tables, and maintenance configs.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
List all Basin Catalogs for your account to audit which buckets are registered and their current state.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/accounts/<account_id>/basin-catalog' \
-H 'Authorization: Bearer <API_TOKEN>' Retrieve credentials for a specific Basin Catalog bucket to configure downstream consumers or data pipelines.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/accounts/<account_id>/basin-catalog/<bucket_name>/credential' \
-H 'Authorization: Bearer <API_TOKEN>' List all tables under a specific namespace to map out the catalog schema before setting maintenance windows.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/accounts/<account_id>/basin-catalog/<bucket_name>/namespaces/<namespace>/tables' \
-H 'Authorization: Bearer <API_TOKEN>'
Adds GET /accounts/{account_id}/basin-catalog to list Basin Catalogs.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds GET /accounts/{account_id}/basin-catalog/{bucket_name} to retrieve Basin Catalog details for a specific bucket. Adds POST /accounts/{account_id}/basin-catalog/{bucket_name}/enable to enable a Basin Catalog. Adds POST /accounts/{account_id}/basin-catalog/{bucket_name}/disable to disable a Basin Catalog. Adds DELETE /accounts/{account_id}/basin-catalog/{bucket_name}/delete to remove Basin Catalog metadata.
+2 more
show less
Adds GET /accounts/{account_id}/basin-catalog/{bucket_name}/credential to retrieve credentials for a Basin Catalog bucket. Adds GET /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces to list namespaces within a Basin Catalog bucket.
7 details in Everything
Cloudflare adds Basin data platform (Catalog, Pipelines, SQL query engine) and a Monetization Gateway for APIs, MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds Basin, a new product for ingesting, managing, and querying analytics data stored in R2, comprising Basin Catalog, Basin Pipelines, and Basin SQL.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Basin SQL, a serverless distributed query engine for data stored in Basin Catalog. Adds Monetization Gateway, enabling monetization policies to charge visitors accessing APIs, MCP tools, web pages, or datasets.
3 details in Everything
Cloudflare: Adds ML-KEM ML-KEM NIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake. ML-DSA ML-DSA NIST's main post-quantum digital signature standard (FIPS 204), formerly Dilithium. It is the planned replacement for RSA and ECDSA signatures on certificates and code. post-quantum post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA.
Adds pending I/O support for Durable Objects, preventing eviction for up to 15 minutes for Workers with a compatibility date of 2026-10-01 or later. Releases Sandbox SDK 1.0, letting a Durable Object control sandbox image, instance size, network access, and lifetime, and save snapshots.
2 details in Everything
└──▷ USE IT
Enable pending I/O in a Durable Object Worker so it can finish background work (e.g. a long write) even after the client disconnects.
wrangler.toml
copy
compatibility_date = "2026-10-01"
Cloudflare launches Basin, a serverless data platform built on Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS.
Introduces Cloudflare Basin: a generally available serverless data platform built on Apache Iceberg and Cloudflare R2 that lets teams ingest, store, catalog, and query analytical data without provisioning or managing infrastructure.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Stores all data in Apache Iceberg open format, allowing any compatible tool to read it directly with no copying, converting, or vendor lock-in. Provides Basin Pipelines, Catalog, and SQL as named components, replacing complex setups such as AWS S3 and Athena with a unified, serverless architecture. Eliminates data egress fees when querying data across different clouds, platforms, or regions.
4 details in Everything
Cloudflare Artifacts enters open beta as a versioned file system for Workers, adding API monitoring and event subscriptions.
Enables programmatic management of Artifacts repositories (create, fork, inspect, read) via an Artifacts binding from a Worker Adds subscription to repository lifecycle events (created, imported, forked, deleted, pushed, cloned, fetched) Allows control of data residency for storage and processing in the US or EU Exposes repository usage metrics (operations, pulls, pushes, errors) via API for analytics
4 details in Everything
Basin Pipelines ingest limit increased to 1 GB/s
Oct 1, 2026
· release notes
Cloudflare Basin Pipelines ingest limit increased from 5 MB/s to 1 GB/s per stream
Account members can self-serve create Account API tokens
Oct 1, 2026
· release notes
Cloudflare allows members with the API Token Provisioning role to self-serve create Account API tokens.
Adds the API Token Provisioning role enabling members to create Account API tokens via Dashboard, API, Terraform, or CF CLI Supports OAuth clients requesting the account_api_tokens:create scope for token creation Restricts created token permissions to the creator's existing access level at the time of creation
3 details in Everything
Introducing Clef: Cloudflare's first open-source decision models, now on Workers AI
Oct 1, 2026
· release notes
Cloudflare Workers AI introduces Clef decision models with REST endpoint and JS binding support
Adds @cf/cloudflare/clef (27B) and @cf/cloudflare/clef-flash (9B), the first open-source decision models on Workers AI that return structured probabilities instead of free-form text. Adds noul, choice, and score question types to the Workers AI input schema for structured state-based decisions.
2 details in Everything
Cloudflare Basin is now generally available
Oct 1, 2026
· release notes
Cloudflare Basin GA brings end-to-end analytics with Pipelines, Catalog, and serverless SQL.
└──▷ USE IT
Initialize a new data pipeline to ingest events from Workers or HTTP endpoints into an Iceberg table.
shell
copy
npx wrangler basin pipelines setup
wrangler basin pipelines setup subcommand initializes a new Basin data pipeline directly from the CLI.Basin SQL engine enables serverless querying of Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS.
2 details in Everything
Web Crypto adds ML-KEM and ML-DSA support
Oct 1, 2026
· release notes
Workers Web Crypto adds ML-KEM ML-KEM NIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake. ML-DSA ML-DSA NIST's main post-quantum digital signature standard (FIPS 204), formerly Dilithium. It is the planned replacement for RSA and ECDSA signatures on certificates and code.
Adds webcrypto_modern_algorithms compatibility flag to enable post-quantum cryptography post-quantum cryptography Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA. Introduces crypto.subtle.generateKey() with algorithm strings ML-KEM-768ML-KEM-768 NIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake. ML-KEM-1024ML-KEM-1024 NIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake. ML-DSA-44, ML-DSA-65ML-DSA-65 NIST's main post-quantum digital signature standard (FIPS 204), formerly Dilithium. It is the planned replacement for RSA and ECDSA signatures on certificates and code. ML-DSA-87ML-DSA-87 NIST's main post-quantum digital signature standard (FIPS 204), formerly Dilithium. It is the planned replacement for RSA and ECDSA signatures on certificates and code. Adds encapsulateBits() and decapsulateBits() methods to SubtleCrypto for ML-KEM key encapsulation. Adds getPublicKey() method and AKP key type support in JSON Web Keys (JWKs) for Workers Web Crypto.
4 details in Everything
Cloudflare AI Search GA adds hybrid search hybrid search Combining keyword search with semantic or vector search. The results use both exact term matches and similarity in meaning. multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. embeddings embeddings Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. OCR OCR Optical character recognition, converting text in an image or scanned document into machine-readable characters. It lets software search or process text that was stored as pixels.
Adds hybrid search as the default index method for new instances, combining semantic vector retrieval with full-text matching Includes Workers AI embedding embedding Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. reranking reranking A model that re-scores a first batch of search results against the query and reorders them, more accurately than the fast first-stage search. Supports @cf/qwen/qwen3-vl-embedding-2b and google-ai-studio/gemini-embedding-2 multimodal embedding models embedding models Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. Enables image inclusion in search and chat requests via the REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Adds OCR availability for scanned PDFs and increases file size limit to 10 MiB for plain-text, code, or OCR-enabled PDFs
+1 more
show less
Makes the type field optional when creating an AI Search instance, inferring website sources from HTTP/HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate.
6 details in Everything
The best way to do MCP auth just got better: Workers OAuth Provider goes v1, with a new split API and full support for MCP 2026-07-28
Oct 1, 2026
· release notes
Workers OAuth Provider v1 introduces a split API with OAuthAuthorizationServer and OAuthResourceServer for decoupled MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds OAuthAuthorizationServer class to @cloudflare/workers-oauth-provider for acting as an authorization server that signs users in and issues tokens Adds OAuthResourceServer class to @cloudflare/workers-oauth-provider for acting as a resource server that validates tokens via Service Binding Adds insufficientScope() function to enable step-up authorization logic in one line Adds support for MCP 2026-07-28 specification including Client ID Metadata Documents Client ID Metadata Documents OAuth 2.0 documents hosted at a client's own URL that declare its identity and redirect URIs, letting authorization servers fetch and verify client metadata without manual registration. Adds purgeExpiredData() method for resumable KV cleanup
+2 more
show less
Adds refreshTokenIdleTTL option for sliding refresh token refresh token A credential used to obtain a new access token without signing in again. It is sent to the authorization service rather than used directly to call the protected API. Adds internal reason field on every error passed to the onError callback
7 details in Everything
Pending I/O operations allow Durable Objects to continue long-running work without a connected client
Oct 1, 2026
· release notes
New compatibility flags durable_object_io_tasks_prevent_eviction and durable_object_io_tasks_do_not_eviction keep Durable Objects alive for pending I/O.
Extends the new keep-alive behavior to service binding requests, remote procedure call (RPC RPC Remote Procedure Call, a protocol that lets a program execute a function on another machine as if it were local, giving cyber tools a structured way to communicate across processes or hosts without managing raw sockets. fetch() , and this.ctx.container.monitor()
1 detail in Everything
Cloudflare launches Sandboxes: isolated Linux microVM containers and Dynamic Workers for running untrusted or agent-generated code︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ USE IT
Run an isolated Linux command in a microVM container to execute untrusted or agent-generated code without sharing a process with your application.
javascript
copy
container.start({
image: "cloudflare/debian-trixie",
entrypoint: ["sleep", "infinity"],
enableInternet: false
});
const process = container.run(["uname", "-a"]);
const output = await process.output();
Load and execute untrusted JavaScript at runtime in an isolated Dynamic Worker, with all outbound network requests blocked.
javascript
copy
const entrypoint = await env.LOADER.load({
compatibilityDate: "2026-09-30",
mainModule: "code.js",
modules: { "code.js": untrustedModule },
globalOutbound: null
}).getEntrypoint<CodeEntrypoint>("Code");
await entrypoint.evaluate();
Adds sandbox containers backed by Durable Objects: a Worker starts a microVM from a named image (e.g., cloudflare/debian-trixie) with its own kernel and network, controlled via container.start with image, entrypoint, and enableInternet fields.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Dynamic Workers via env.LOADER.load with compatibilityDate, mainModule, modules, and globalOutbound fields, enabling runtime creation of isolated Workers that run untrusted JavaScript, Python, or WebAssembly WebAssembly A binary instruction format that runs in browsers and server runtimes at near-native speed, letting developers compile C, Rust, or other languages into a portable, sandboxed module any compliant host can execute. Supports mounting R2 buckets into sandbox container workspaces and keeping files between instances via snapshots. Supports browser-accessible web servers running inside a sandbox container, enabling live application previews. Adds sandbox management APIs for listing a user's sandboxes and recording when and why each one stops.
+1 more
show less
Supports running coding agents (such as Claude Code, Codex, and Devin) inside per-task sandboxes.
6 details in Everything
Cloudflare Containers adds Durable Object Container API with TypeScript/JavaScript SDK for managing containerized workloads︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ USE IT
Proxy an incoming worker request to a container process listening on port 8080, starting it first if not already running.
src/index.js
copy
import { DurableObject } from 'cloudflare:workers';
import { rewriteRequestForContainer, startAndWaitForPort } from './utils';
export class MyContainer extends DurableObject {
async fetch(request) {
const container = this.ctx.container;
await startAndWaitForPort(container, { port: 8080, inactivityTimeout: 300 * 1000 });
const forwarded = rewriteRequestForContainer(request);
const response = await container.getTcpPort(8080).fetch(forwarded);
return response;
}
}
Declare a container-backed Durable Object with SQLite storage in wrangler.toml so Cloudflare routes requests to the right container instance.
wrangler.toml
copy
[[durable_objects.bindings]]
name = "MY_CONTAINER"
class_name = "MyContainer"
[[migrations]]
tag = "2026-09-30"
[[exports]]
type = "durable-object"
storage = "sqlite"
Route an incoming request to a per-session container by name, so each user session gets its own isolated container instance.
src/index.js
copy
export default {
async fetch(request, env) {
const url = new URL(request.url);
const sessionId = url.searchParams.get('session');
const containerRequest = request.clone();
return env.MY_CONTAINER.getByName(sessionId).fetch(containerRequest);
}
}
Adds ctx.container property on Durable Objects to access a container instance directly from TypeScript/JavaScript worker code.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds startAndWaitForPort(container, { port, inactivityTimeout }) utility to start a container and poll its /health endpoint until ready. Adds rewriteRequestForContainer(request) utility to rewrite worker requests for forwarding to a container's internal HTTP endpoint. Adds container.getTcpPort(port) method to obtain a handle for issuing HTTP requests to a specific port on a running container. Adds container.setInactivityTimeout(duration) method to configure automatic container shutdown after a period of inactivity.
+5 more
show less
Adds container.start() method to programmatically launch a container from within Durable Object code. Adds container.running boolean property to check whether a container instance is currently active before attempting a start. Supports wrangler.toml Durable Object export with type = 'durable-object' and storage = 'sqlite' for container-backed objects. Supports scheduling policies to choose whether image and instance configuration is managed centrally or from Durable Object code. Enables env.<Namespace>.getByName(sessionId) routing so each named session is pinned to its own container-backed Durable Object.
10 details in Everything
Cloudflare launches cf, a unified CLI with 2,900+ API commands, cloudflare.config.ts config, and plain-language command search.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Discover the right Cloudflare API command when you know what you want to do but not the exact subcommand.
copy
$ cf cli search 'create a DNS A record' Migrate an existing Wrangler project to cf tooling so you can use cf dev, cf build, and cf deploy.
Bootstrap a new Workers project with typed cloudflare.config.ts configuration and deploy it.
copy
$ cf init my-worker && cd my-worker && cf deploy
Introduces cf, a new unified CLI installable via npm install --global cf, yarn global add cf, pnpm add --global cf, or bun add --global cf, covering both the public Cloudflare API and Workers projects.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Provides 2,900+ commands generated from Cloudflare API schemas, enabling management of zones, DNS, storage, and security settings from the command line. Adds cloudflare.config.ts as the typed project configuration format for Workers projects, enabling editor and agent autocomplete for bindings and triggers. Adds cf dev, cf build, and cf deploy commands that delegate to the project's framework, the Cloudflare Vite plugin, or Wrangler depending on the project. Adds cf cli search subcommand for plain-language command discovery — describe a task in plain English to find the right command.
+2 more
show less
Adds cf init to create a Workers project and cf migrate to convert an existing Wrangler project (wrangler.jsonc / wrangler.toml) to cloudflare.config.ts. Supports coding-agent and CI/automation workflows, with API-token authentication for running cf in pipelines.
7 details in Everything
Cloudflare adds Container snapshot/restore, durable_object scheduling, cache invalidation, multi-client Browser sessions, and richer Zero Trust network log fields︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ USE IT
Configure a Durable Object to pick its own container image and instance size at runtime, using a custom Dockerfile.
wrangler.toml
copy
[[containers]]
class_name = "AgentComputer"
scheduling_policy = "durable_object"
[containers.images]
[containers.images.base]
dockerfile = "./container/Dockerfile"
Invalidate all assets sharing a cache tag so unchanged content is revalidated rather than re-downloaded from origin.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/zones/<zone_id>/invalidate_cache' \
-H 'Authorization: Bearer <token>' \
-H 'Content-Type: application/json' \
-d '{"tags":["product-images"]}' Trace every session where a Worker reached a service behind a Mesh node and identify exactly which cloudflared replica served it.
copy
$ SELECT SourceName, DestinationReplicaID, DestinationTunnelID
FROM zero_trust_network_sessions
WHERE OnrampType = 'WORKERS_VPC' AND Offramp = 'MESH'
Adds scheduling_policy = "durable_object" to [[containers]] in Wrangler config, letting a Durable Object select the container image and instance size at runtime via ctx.container.images and ctx.container.start({ image, instance }) .︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds support for the cloudflare/debian-trixie Cloudflare-managed image (Node.js 24.20.0 on Debian Trixie slim) usable with the durable_object scheduling policy without configuring a named image. Adds snapshotContainer() to the Durable Object Container API (public beta) to capture a full container filesystem, storable and passable back to start({ containerSnapshot }) to restore state after sleep, restart, or Durable Object handoff. Adds a POST /invalidate_cache API endpoint and an Invalidate Cache action in the Caching > Configuration dashboard page, marking content stale and revalidating with the origin on the next request instead of forcing a full purge; supports URLs, cache tags, hostnames, URL prefixes, and everything selectors. Adds five new fields — OnrampType, Offramp , SourceName, SourceID, and DestinationReplicaID — to the zero_trust_network_sessions dataset in Zero Trust Network Session Logs, distinguishing Mesh nodes, Workers VPC VPC A logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware. cloudflared tunnel replicas.
+4 more
show less
Adds Traffic Source column to Zero Trust > Insights & Logs > Network logs dashboard view, surfacing MESH, WORKERS_VPC, CF1_CLIENT, MAGIC, and OTHER traffic origins. Enables multiple concurrent puppeteer.connect() CDP CDP Cisco Discovery Protocol, a Cisco-proprietary Layer 2 protocol that advertises device identity, capabilities, and topology between directly connected Cisco gear, giving cyber tools a passive way to map network infrastructure. @cloudflare/puppeteer version 1.1.0 or later. Removes the 2 GB disk-per-GiB-memory ratio limit on custom Container instance types, allowing up to 20 GB of disk (disk_mb = 20_000) on any custom instance regardless of memory, enabling large images, datasets, and build caches. Adds AI Gateway User Insights analysis — task-grouped conversations, conversation turn tracking, model-fit comparison with cost and latency, and a Potential Savings view surfacing requests that may work with cheaper/faster models.
Adds scheduling_policy = "durable_object" to [[containers]] in Wrangler config, letting a Durable Object select the container image and instance size at runtime via ctx.container.images and ctx.container.start({ image, instance }) .︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds support for the cloudflare/debian-trixie Cloudflare-managed image (Node.js 24.20.0 on Debian Trixie slim) usable with the durable_object scheduling policy without configuring a named image. Adds snapshotContainer() to the Durable Object Container API (public beta) to capture a full container filesystem, storable and passable back to start({ containerSnapshot }) to restore state after sleep, restart, or Durable Object handoff. Adds a POST /invalidate_cache API endpoint and an Invalidate Cache action in the Caching > Configuration dashboard page, marking content stale and revalidating with the origin on the next request instead of forcing a full purge; supports URLs, cache tags, hostnames, URL prefixes, and everything selectors. Adds AI Gateway User Insights analysis — task-grouped conversations, conversation turn tracking, model-fit comparison with cost and latency, and a Potential Savings view surfacing requests that may work with cheaper/faster models.
4 more in Everything
└──▷ BREAKING ON UPGRADE
! Purge requests (by cache tag, hostname, prefix, or everything) now force a cache miss for Cache Reserve content instead of marking it for revalidation. The next request after a purge triggers a full origin fetch and a billable Cache Reserve Class A write, even if the content has not changed.
Cloudflare adds Containers API, Threat Signals intelligence API, and environment-scoped cache invalidation endpoints.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Trigger a cache purge scoped to a specific deployment environment without blowing out the entire zone cache.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/zones/{zone_id}/environments/{environment_id}/invalidate_cache' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' \
-d '{"purge_everything": true}' Search Cloudforce One threat intelligence articles with AI Search to find relevant adversary TTPs TTPs Tactics, techniques and procedures, the goals, methods and specific behaviors used by an attacker. They describe how an attack works, rather than only the files or addresses it leaves behind.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/{account_id}/cloudforce-one/v2/threat-signals/search' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' \
-d '{"query": "ransomware lateral movement techniques"}' Retrieve a JWT JWT An open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object passed between parties. Cyber tools use it to verify identity and permissions without querying a central session store. embedding embedding Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/{account_id}/containers/registries/{domain}/credentials' \
-H 'Authorization: Bearer <API_TOKEN>'
Adds POST /zones/{zone_id}/invalidate_cache and POST /zones/{zone_id}/environments/{environment_id}/invalidate_cache to invalidate cached content globally or scoped to a specific environment.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Containers API under /accounts/{account_id}/containers/applications with endpoints to list, create, get, modify, and delete containerized applications. Adds /accounts/{account_id}/containers/applications/{application_id}/instances-v2 for listing container instances, alongside the deprecated /instances endpoint. Adds /accounts/{account_id}/containers/applications/{application_id}/rollouts to create and manage application rollouts. Adds /accounts/{account_id}/containers/applications/{application_id}/versions to list all application versions.
+14 more
show less
Adds /accounts/{account_id}/containers/image-preparations to prepare a container image prior to deployment. Adds container registry management endpoints at /accounts/{account_id}/containers/registries to list, configure, and delete private external image registries. Adds /accounts/{account_id}/containers/registries/{domain}/credentials to generate a JWT for authenticating against a specified image registry. Adds Threat Signals API under /accounts/{account_id}/cloudforce-one/v2/threat-signals for managing threat intelligence feeds, articles, indicators, and AI skills in Cloudforce One; requires an API token with Cloudforce One permissions. Adds POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/search to search Threat Signals articles using AI Search. Adds /accounts/{account_id}/cloudforce-one/v2/threat-signals/categories to list Threat Signals feed categories. Adds full CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. /accounts/{account_id}/cloudforce-one/v2/threat-signals/feeds, plus POST /feeds/poll to trigger a feed poll and GET /feeds/{feed_id}/raw to retrieve feed XML. Adds /accounts/{account_id}/cloudforce-one/v2/threat-signals/feeds/{feed_id}/skills to get and set AI skills associated with a feed. Adds article management endpoints under /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles to list, get, bulk-update, and update read status of threat intelligence articles. Adds /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/content to retrieve full article content. Adds tag management endpoints at /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/tags and POST /articles/{article_id}/tag to add, remove, and AI-generate article tags. Adds /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/skills/{skill_id}/output to retrieve AI skill output for a specific article. Adds /accounts/{account_id}/cloudforce-one/v2/threat-signals/indicators to list article indicators. Adds full CRUD endpoints for Threat Signals AI skills at /accounts/{account_id}/cloudforce-one/v2/threat-signals/skills, including tag-category management at /skills/{skill_id}/tag-categories.
19 details in Everything
Cloudflare adds a dedicated CLI for managing resources and a Sandboxes offering for isolated execution via Containers and Dynamic Workers.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
New Cloudflare CLI lets practitioners manage Cloudflare resources from a single command-line interface.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New Sandboxes capability provides isolated execution on Cloudflare using Containers and Dynamic Workers.
2 details in Everything
Cloudflare: Adds snapshot and restore APIs (public beta) to persist a point-in-time Container filesystem.
Allocates up to 20 GB of disk to any custom Container instance type, independent of memory, removing the previous disk-to-memory ratio limit. Enables multiple Workers to share one Browser Run session via concurrent connections. Network logs now identify Cloudflare Mesh and Workers VPC VPC A logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware. cloudflared replica received each session. Adds User Insights to identify which tasks drive AI model usage and surface where faster or less expensive models may work.
Adds User Insights to identify which tasks drive AI model usage and surface where faster or less expensive models may work.
3 more in Everything
WAF - WAF Release - 2026-09-30 (2026-09-30)
Sep 30, 2026
·
issue 091
Snapshot and restore Container filesystem
Sep 30, 2026
· release notes
Public beta for Container snapshot and restore via Durable Object Container API
Introduces the snapshotContainer() method on this.ctx.container to capture a full Container filesystem state. Enables passing a saved containerSnapshot handle to the start() method's containerSnapshot argument to restore that state.
2 details in Everything
Sandbox SDK 1.0: control every sandbox from your own Durable Object
Sep 30, 2026
· release notes
Sandbox SDK 1.0 allows Durable Objects to control sandbox containers via ctx.container API with public beta snapshots.
Adds ctx.container access in DurableObject constructor for direct sandbox lifecycle management Adds container.start() method to configure image, instance size (e.g., lite ), and network access per start Adds container.exec() for running commands with streamed I/O inside the sandbox
3 details in Everything
Role-based access control for Browser Isolation policies
Sep 30, 2026
· release notes
Cloudflare Browser Isolation policies now support role-based access control role-based access control Role-based access control, where permissions are assigned to roles such as reader or administrator and users receive those roles. It makes access easier to manage than individual permission lists.
Introduces the Zero Trust HTTP Policies Admin account-level role to grant access to all HTTP policies in an account. Enables resource-scoped roles to let a team member manage a specific isolation policy without exposing other Gateway resources.
2 details in Everything
Transformers are now generally available
Sep 30, 2026
· release notes
Cloudflare Logpush Transformers GA: filter, reshape, redact logs via SQL before delivery
Adds Transformer Studio UI and Cloudflare API for creating and previewing Logpush transformers with SQL queries against NDJSON NDJSON A text format where each line is a self-contained JSON object, making it easy to stream, append, and parse large datasets record-by-record without loading the whole file into memory. Enables attaching named SQL Transformer queries to account-scoped or zone-scoped Logpush jobs to filter, reshape, redact, or compute fields before delivery.
2 details in Everything
New scheduling policy for Containers to configure image and instance from Durable Objects
Sep 30, 2026
· release notes
Cloudflare Containers adds durable_object scheduling policy for dynamic image and instance configuration
scheduling_policy in Wrangler configuration now accepts durable_object to enable runtime customization of Container images and sizes.this.ctx.container.images exposes immutable image references from the Durable Object context for use in start() .image and instance arguments accepted by ctx.container.start() allow specifying the container image and instance size at runtime.
3 details in Everything
Cloudflare One Client for Windows (version 2026.8.2033.1)
Sep 30, 2026
· release notes
Adds unrestricted LAN inclusion policy to route non-RFC 1918 RFC 1918 IETF standard that reserves three IPv4 address ranges (10.x, 172.16–31.x, 192.168.x) for private networks, never routed on the public internet, giving tools a reliable way to identify internal traffic.
Pay for AI inference with Machine Payments
Sep 30, 2026
· release notes
Cloudflare AI Gateway adds beta Machine Payments via x402 x402 A proposed HTTP payment protocol revival using status code 402, enabling machine-to-machine micropayments over HTTP so cyber tools can gate API access or resources behind automated, per-request cryptocurrency payments.
Adds support for the x402 payment protocol on the /ai/run endpoint, allowing clients to pay with stablecoin wallets instead of prepaid credits by setting the Payment-Method: x402 header.
1 detail in Everything
API surface changed: +30 endpoints, 27 modified, 15 deprecated︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
API change API surface changed: +30 endpoints, 27 modified, 15 deprecated︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
+ DELETE /accounts/{account_id}/access/identity_providers/{identity_provider_id}/scim/groups/{group_id} + DELETE /accounts/{account_id}/access/identity_providers/{identity_provider_id}/scim/users/{user_id} + DELETE /accounts/{account_id}/dns_settings/nameserver_sets/{nameserver_set_id} + GET /accounts/{account_id}/access/identity_providers/{identity_provider_id}/scim/groups/{group_id} + GET /accounts/{account_id}/access/identity_providers/{identity_provider_id}/scim/users/{user_id} + GET /accounts/{account_id}/basin-catalog + GET /accounts/{account_id}/basin-catalog/{bucket_name} + GET /accounts/{account_id}/basin-catalog/{bucket_name}/maintenance-configs + GET /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces + GET /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces/{namespace}/tables + GET /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name} + GET /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs + GET /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-runs + GET /accounts/{account_id}/dns_settings/nameserver_sets + GET /accounts/{account_id}/dns_settings/nameserver_sets/{nameserver_set_id} + GET /accounts/{account_id}/security-center/partners/{partner}/settings + GET /accounts/{account_id}/security-center/partners/{partner}/shadow-zones + GET /accounts/{account_id}/security-center/partners/{partner}/shadow-zones/{domain}/hosts + GET /zones/{zone_id}/security-center/partners/{partner}/shadow-hosts + POST /accounts/{account_id}/basin-catalog/{bucket_name}/credential + POST /accounts/{account_id}/basin-catalog/{bucket_name}/delete + POST /accounts/{account_id}/basin-catalog/{bucket_name}/disable + POST /accounts/{account_id}/basin-catalog/{bucket_name}/enable + POST /accounts/{account_id}/basin-catalog/{bucket_name}/maintenance-configs + POST /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs + POST /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs/{configuration_type}/queue + POST /accounts/{account_id}/dns_settings/nameserver_sets + POST /accounts/{account_id}/security-center/partners/{partner}/settings + POST /zones/{zone_id}/environments/{environment_id}/invalidate_cache + POST /zones/{zone_id}/invalidate_cache
~ DELETE /accounts/{account_id}/workers/dispatch/namespaces/{dispatch_namespace}/scripts: param tags (query) now required ~ GET /accounts/{account_id}/abuse-reports: response schema changed ~ GET /accounts/{account_id}/abuse-reports/submitted: response schema changed ~ GET /accounts/{account_id}/abuse-reports/submitted/{report_id}: response schema changed ~ GET /accounts/{account_id}/abuse-reports/submitted/{report_id}/emails: response schema changed ~ GET /accounts/{account_id}/abuse-reports/{report_id}/appeals/eligibility: response schema changed ~ GET /accounts/{account_id}/abuse-reports/{report_id}/emails: response schema changed ~ GET /accounts/{account_id}/abuse-reports/{report_id}/mitigations: response schema changed ~ GET /accounts/{account_id}/abuse-reports/{report_param}: response schema changed ~ GET /accounts/{account_id}/registrar/domains: response schema changed ~ GET /accounts/{account_id}/registrar/domains/{domain_name}: response schema changed ~ PATCH /accounts/{account_id}/magic/sites/{site_id}: request body changed ~ PATCH /accounts/{account_id}/magic/sites/{site_id}/lans/{lan_id}: request body changed ~ PATCH /accounts/{account_id}/magic/sites/{site_id}/wans/{wan_id}: request body changed ~ POST /accounts/{account_id}/abuse-reports/{report_id}/mitigations/appeal: response schema changed ~ POST /accounts/{account_id}/abuse-reports/{report_param}: response schema changed ~ POST /accounts/{account_id}/access/organizations: request body changed ~ POST /accounts/{account_id}/email-security/investigate/release: request body changed ~ POST /accounts/{account_id}/magic/sites/{site_id}/wans: request body changed ~ POST /accounts/{account_id}/pages/projects/{project_name}/source: request body changed ~ POST /zones/{zone_id}/access/organizations: request body changed ~ PUT /accounts/{account_id}/access/organizations: request body changed ~ PUT /accounts/{account_id}/magic/sites/{site_id}: request body changed ~ PUT /accounts/{account_id}/magic/sites/{site_id}/lans/{lan_id}: request body changed ~ PUT /accounts/{account_id}/magic/sites/{site_id}/wans/{wan_id}: request body changed ~ PUT /accounts/{account_id}/registrar/domains/{domain_name}: response schema changed ~ PUT /zones/{zone_id}/access/organizations: request body changed
⚠ GET /accounts/{account_id}/r2-catalog ⚠ GET /accounts/{account_id}/r2-catalog/{bucket_name} ⚠ GET /accounts/{account_id}/r2-catalog/{bucket_name}/maintenance-configs ⚠ GET /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces ⚠ GET /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables ⚠ GET /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name} ⚠ GET /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs ⚠ GET /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-runs ⚠ POST /accounts/{account_id}/r2-catalog/{bucket_name}/credential ⚠ POST /accounts/{account_id}/r2-catalog/{bucket_name}/delete ⚠ POST /accounts/{account_id}/r2-catalog/{bucket_name}/disable ⚠ POST /accounts/{account_id}/r2-catalog/{bucket_name}/enable ⚠ POST /accounts/{account_id}/r2-catalog/{bucket_name}/maintenance-configs ⚠ POST /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs ⚠ POST /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs/{configuration_type}/queue
New endpoint DELETE /accounts/{account_id}/access/identity_providers/{identity_provider_id}/scim/groups/{group_id}︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New endpoint DELETE /accounts/{account_id}/access/identity_providers/{identity_provider_id}/scim/users/{user_id} New endpoint DELETE /accounts/{account_id}/dns_settings/nameserver_sets/{nameserver_set_id} New endpoint GET /accounts/{account_id}/access/identity_providers/{identity_provider_id}/scim/groups/{group_id} New endpoint GET /accounts/{account_id}/access/identity_providers/{identity_provider_id}/scim/users/{user_id}
+25 more
show less
New endpoint GET /accounts/{account_id}/basin-catalog New endpoint GET /accounts/{account_id}/basin-catalog/{bucket_name} New endpoint GET /accounts/{account_id}/basin-catalog/{bucket_name}/maintenance-configs New endpoint GET /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces New endpoint GET /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces/{namespace}/tables New endpoint GET /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name} New endpoint GET /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs New endpoint GET /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-runs New endpoint GET /accounts/{account_id}/dns_settings/nameserver_sets New endpoint GET /accounts/{account_id}/dns_settings/nameserver_sets/{nameserver_set_id} New endpoint GET /accounts/{account_id}/security-center/partners/{partner}/settings New endpoint GET /accounts/{account_id}/security-center/partners/{partner}/shadow-zones New endpoint GET /accounts/{account_id}/security-center/partners/{partner}/shadow-zones/{domain}/hosts New endpoint GET /zones/{zone_id}/security-center/partners/{partner}/shadow-hosts New endpoint POST /accounts/{account_id}/basin-catalog/{bucket_name}/credential New endpoint POST /accounts/{account_id}/basin-catalog/{bucket_name}/delete New endpoint POST /accounts/{account_id}/basin-catalog/{bucket_name}/disable New endpoint POST /accounts/{account_id}/basin-catalog/{bucket_name}/enable New endpoint POST /accounts/{account_id}/basin-catalog/{bucket_name}/maintenance-configs New endpoint POST /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs New endpoint POST /accounts/{account_id}/basin-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs/{configuration_type}/queue New endpoint POST /accounts/{account_id}/dns_settings/nameserver_sets New endpoint POST /accounts/{account_id}/security-center/partners/{partner}/settings New endpoint POST /zones/{zone_id}/environments/{environment_id}/invalidate_cache New endpoint POST /zones/{zone_id}/invalidate_cache
30 details in Everything
└──▷ BREAKING ON UPGRADE
! DELETE /accounts/{account_id}/workers/dispatch/namespaces/{dispatch_namespace}/scripts: param tags (query) now required! Deprecated endpoint GET /accounts/{account_id}/r2-catalog (still works)! Deprecated endpoint GET /accounts/{account_id}/r2-catalog/{bucket_name} (still works)! Deprecated endpoint GET /accounts/{account_id}/r2-catalog/{bucket_name}/maintenance-configs (still works)! Deprecated endpoint GET /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces (still works)! Deprecated endpoint GET /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables (still works)! Deprecated endpoint GET /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name} (still works)! Deprecated endpoint GET /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs (still works)! Deprecated endpoint GET /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-runs (still works)! Deprecated endpoint POST /accounts/{account_id}/r2-catalog/{bucket_name}/credential (still works)! Deprecated endpoint POST /accounts/{account_id}/r2-catalog/{bucket_name}/delete (still works)! Deprecated endpoint POST /accounts/{account_id}/r2-catalog/{bucket_name}/disable (still works)! Deprecated endpoint POST /accounts/{account_id}/r2-catalog/{bucket_name}/enable (still works)! Deprecated endpoint POST /accounts/{account_id}/r2-catalog/{bucket_name}/maintenance-configs (still works)! Deprecated endpoint POST /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs (still works)! Deprecated endpoint POST /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs/{configuration_type}/queue (still works)
Identify Mesh, Workers VPC, and Cloudflare Tunnel replicas in network logs
Sep 29, 2026
· release notes
Cloudflare Network Logs now distinguish Mesh and Workers VPC VPC A logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware.
Zero Trust Network Session Logs (zero_trust_network_sessions dataset) include OnrampType, Offramp , SourceName, SourceID, and DestinationReplicaID fields for Mesh and Workers VPC traffic. Gateway network logs in the UI expose Traffic Source and Traffic Destination columns to identify Cloudflare Mesh nodes, AI agents, and Cloudflare Tunnel replicas.
2 details in Everything
Cloudflare One Client for macOS (version 2026.8.2028.1)
Sep 29, 2026
· release notes
Cloudflare One Client for macOS beta adds non-RFC1918 RFC1918 IETF standard that reserves three IPv4 address ranges (10.x, 172.16–31.x, 192.168.x) for private networks, never routed on the public internet, giving tools a reliable way to identify internal traffic.
Adds support for routing non-RFC 1918 local IPv4 networks through the WARP tunnel when unrestricted LAN inclusion is enabled by policy or MDM
1 detail in Everything
Connect multiple clients to one Browser Run session
Sep 29, 2026
· release notes
Browser Run now accepts multiple concurrent client connections in a single session.
Enables puppeteer.connect(env.MYBROWSER, sessionId) to share one Browser Run session across multiple Workers Supports creating isolated pages via browser.createBrowserContext() and context.newPage() within the shared session Requires @cloudflare/puppeteer version 1.1.0 or later for concurrent connection support
3 details in Everything
Workers Cache — mark cached responses stale with invalidate()
Sep 29, 2026
· release notes
Workers Cache adds invalidate() to mark cached responses stale instead of deleting them.
Custom Container instance types no longer have a disk to memory ratio limit
Sep 29, 2026
· release notes
Custom Container instances can now allocate up to 20 GB of disk regardless of memory size.
Removes the previous 2 GB disk-per-1 GiB memory limit on Custom Container instance types, allowing any type to use up to 20 GB of disk space. Increases the maximum image size for Custom Containers to match the instance disk allocation (up to 20 GB), enabling deployment of larger container images, datasets, or build caches.
2 details in Everything
Identify model overuse and potential savings with User Insights
Sep 29, 2026
· release notes
AI Gateway User Insights adds model overuse detection and potential savings analysis capabilities.
User Insights now groups conversations by task to track conversation turns and compare model fit with cost and latency Adds the Potential Savings view in AI Gateway to highlight requests that may work with faster or less expensive models without compromising output quality
2 details in Everything
Cloudflare One Client for Windows (version 2026.8.2028.1)
Sep 29, 2026
· release notes
Cloudflare One Client adds unrestricted LAN inclusion support and Windows service auto-recovery for beta.
Adds unrestricted LAN inclusion policy/MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies. RFC 1918 RFC 1918 IETF standard that reserves three IPv4 address ranges (10.x, 172.16–31.x, 192.168.x) for private networks, never routed on the public internet, giving tools a reliable way to identify internal traffic.
1 detail in Everything
Cloudflare: Adds exports field to Wrangler configuration for declaring Workflows a Worker defines, accepting type, name, limits, schedules, and default_retention — requires Wrangler 4.139.0 or above.
└──▷ TRY IT
Track Browser Run crawl job progress in real time by subscribing lifecycle events to a Cloudflare Queue instead of polling.
copy
$ wrangler queues subscription create my-crawl-events --source browserRun --events crawl.started,crawl.updated,crawl.finished Scope an email suppression to a single sending domain so a bounce on mail.myappexample.com does not block the recipient across your whole account.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/<ACCOUNT_ID>/email/sending/suppressions' \
-H 'Authorization: Bearer <TOKEN>' \
-H 'Content-Type: application/json' \
-d '{"email": "user@example.net", "scope": {"type": "sending_domain", "value": "mail.myappexample.com"}}' Declare a Workflow in Wrangler config so it is created on deploy without requiring a binding, and schedule it to run hourly.
wrangler.toml
copy
[exports.MyWorkflow]
type = "workflow"
name = "my-workflow"
schedules = ["0 * * * *"]
Adds ctx.exports so a Worker can call Workflows it declares in exports by class name using the same API as a Workflow binding, without needing a separate binding — requires Wrangler 4.142.0, @cloudflare/vite-plugin 1.61.0, or @cloudflare/vitest-plugin 1.3.0 or above. Extends WebMCP support to Kitesurf sessions (in addition to Lab sessions), using the document.modelContext API; adds --category-experimental-webmcp flag to Chrome DevTools MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. list_webmcp_tools and execute_webmcp_tool tools; Lab sessions no longer expose navigator.modelContextTesting. Adds a product-level R2 bandwidth usage metrics page in the Cloudflare dashboard, split by object upload and download per bucket or across all buckets, with the same data exposed via the GraphQL Analytics API. Adds RFC 8509 RFC 8509 An IETF standards document specifying a mechanism for DNS resolvers to signal which root key signing keys they trust, letting operators detect mismatches during DNSSEC root key rollovers. root-key-sentinel-is-ta-38696.dnstest.dev) to verify whether the resolver trusts a DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit.
Adds ctx.exports so a Worker can call Workflows it declares in exports by class name using the same API as a Workflow binding, without needing a separate binding — requires Wrangler 4.142.0, @cloudflare/vite-plugin 1.61.0, or @cloudflare/vitest-plugin 1.3.0 or above. Adds a product-level R2 bandwidth usage metrics page in the Cloudflare dashboard, split by object upload and download per bucket or across all buckets, with the same data exposed via the GraphQL Analytics API. Adds RFC 8509 RFC 8509 An IETF standards document specifying a mechanism for DNS resolvers to signal which root key signing keys they trust, letting operators detect mismatches during DNSSEC root key rollovers. root-key-sentinel-is-ta-38696.dnstest.dev) to verify whether the resolver trusts a DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit.
1 more in Everything
Cloudflare API v7.11.0 adds Managed Defense vulnerability scanning, zone tracing, Hyperdrive restart, SFU SFU A Selective Forwarding Unit: a media server architecture that relays incoming WebRTC streams to other participants without decoding them, reducing server CPU cost and latency in multi-party video or data pipelines.
└──▷ TRY IT
Retrieve a reviewed vulnerability report for a specific scan after Managed Defense discovers issues in your repository.
copy
$ curl -s -X GET 'https://api.cloudflare.com/client/v4/accounts/{account_id}/managed-defense/vulnerability-discovery/scans/{scan_id}/report' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' Enable and inspect zone-level request tracing settings to debug traffic flows through Cloudflare.
copy
$ curl -s -X GET 'https://api.cloudflare.com/client/v4/zones/{zone_id}/observability/tracing/settings' \
-H 'Authorization: Bearer <API_TOKEN>' Restart a stalled Hyperdrive instance without reprovisioning its full config.
copy
$ curl -s -X POST 'https://api.cloudflare.com/client/v4/accounts/{account_id}/hyperdrive/configs/{hyperdrive_id}/restart' \
-H 'Authorization: Bearer <API_TOKEN>'
Adds GET/PUT/DELETE /zones/{zone_id}/observability/tracing/settings and GET/PUT/DELETE /zones/{zone_id}/observability/tracing/rules endpoints to view, update, reset, and manage trace rules for a zone.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds GET /accounts/{account_id}/managed-defense/vulnerability-discovery/repos and POST /accounts/{account_id}/managed-defense/vulnerability-discovery/repos endpoints to list and create vulnerability-discovery repositories under Cloudflare Managed Defense. Adds GET /accounts/{account_id}/managed-defense/vulnerability-discovery/scans and GET /accounts/{account_id}/managed-defense/vulnerability-discovery/scans/{scan_id}/report endpoints to retrieve vulnerability scans and reviewed vulnerability reports. Adds GET /accounts/{account_id}/managed-defense/vulnerability-discovery/repos/{repo_id}/scans/{scan_id}/report endpoint to retrieve a reviewed vulnerability report scoped to a specific repository. Adds POST /accounts/{account_id}/hyperdrive/configs/{hyperdrive_id}/restart endpoint to restart a Hyperdrive instance.
+14 more
show less
Adds POST /accounts/{account_id}/registrar/domain-transfer-check endpoint to check domain transfer eligibility. Adds POST /accounts/{account_id}/registrar/registrations/{domain_name}/transfer-in and GET /accounts/{account_id}/registrar/registrations/{domain_name}/transfer-in-status endpoints to initiate and monitor inbound domain transfers. Adds PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{member_account_id} and DELETE counterpart to add and remove account memberships from an Address Map. Adds SFU app management endpoints to retrieve, create, update, and delete SFU apps, plus endpoints to list, create, and update TURN keys. Adds AI Search instance endpoints to create and update AI Search instances, including support for the Search for Agents default namespace. Adds Cloudflare AI Gateway management endpoints to list, get, create, update, and delete gateways, plus dynamic route CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. Adds provider key and custom provider endpoints to store and retrieve AI Gateway provider keys and custom providers. Adds posture rule and posture integration CRUD endpoints, plus device settings get, update, and reset endpoints. Adds R2 bucket operations including Set Object Lifecycle Rules , Set Bucket CORS Policy , Set Bucket Lock Rules , and event notification rule endpoints. Adds Move account to organization , List organization accounts , Get tenant details , and List tenant account types account/org management endpoints. Adds PhishGuard endpoints to list reports, batch allow/block/trusted-domain operations, list impersonation registry entries, and list reclassify submissions. Adds Apply Email Routing settings and Unlock Email Routing DNS records endpoints. Adds Cloudflare Pages full CRUD endpoints for projects, deployments, custom domains, and build cache purge, including Retry a Pages deployment and Roll back a Pages deployment . Bumps the cloudflare-go SDK to v7.11.0 (go get -u github.com/cloudflare/cloudflare-go/v7@v7.11.0).
Adds GET/PUT/DELETE /zones/{zone_id}/observability/tracing/settings and GET/PUT/DELETE /zones/{zone_id}/observability/tracing/rules endpoints to view, update, reset, and manage trace rules for a zone.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds GET /accounts/{account_id}/managed-defense/vulnerability-discovery/repos and POST /accounts/{account_id}/managed-defense/vulnerability-discovery/repos endpoints to list and create vulnerability-discovery repositories under Cloudflare Managed Defense. Adds GET /accounts/{account_id}/managed-defense/vulnerability-discovery/scans and GET /accounts/{account_id}/managed-defense/vulnerability-discovery/scans/{scan_id}/report endpoints to retrieve vulnerability scans and reviewed vulnerability reports. Adds GET /accounts/{account_id}/managed-defense/vulnerability-discovery/repos/{repo_id}/scans/{scan_id}/report endpoint to retrieve a reviewed vulnerability report scoped to a specific repository. Adds POST /accounts/{account_id}/hyperdrive/configs/{hyperdrive_id}/restart endpoint to restart a Hyperdrive instance.
+13 more
show less
Adds POST /accounts/{account_id}/registrar/domain-transfer-check endpoint to check domain transfer eligibility. Adds POST /accounts/{account_id}/registrar/registrations/{domain_name}/transfer-in and GET /accounts/{account_id}/registrar/registrations/{domain_name}/transfer-in-status endpoints to initiate and monitor inbound domain transfers. Adds PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{member_account_id} and DELETE counterpart to add and remove account memberships from an Address Map. Adds SFU app management endpoints to retrieve, create, update, and delete SFU apps, plus endpoints to list, create, and update TURN keys. Adds AI Search instance endpoints to create and update AI Search instances, including support for the Search for Agents default namespace. Adds Cloudflare AI Gateway management endpoints to list, get, create, update, and delete gateways, plus dynamic route CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. Adds provider key and custom provider endpoints to store and retrieve AI Gateway provider keys and custom providers. Adds posture rule and posture integration CRUD endpoints, plus device settings get, update, and reset endpoints. Adds R2 bucket operations including Set Object Lifecycle Rules , Set Bucket CORS Policy , Set Bucket Lock Rules , and event notification rule endpoints. Adds Move account to organization , List organization accounts , Get tenant details , and List tenant account types account/org management endpoints. Adds PhishGuard endpoints to list reports, batch allow/block/trusted-domain operations, list impersonation registry entries, and list reclassify submissions. Adds Apply Email Routing settings and Unlock Email Routing DNS records endpoints. Adds Cloudflare Pages full CRUD endpoints for projects, deployments, custom domains, and build cache purge, including Retry a Pages deployment and Roll back a Pages deployment .
1 more in Everything
Cloudflare adds WebMCP to Browser Run, new Workers tracing APIs, crawl event subscriptions via Queues Queues Data structures that hold items in order for processing, typically first-in-first-out; cyber tools use them to buffer events or tasks between pipeline stages without dropping data under load.
└──▷ USE IT
Annotate the current tracing span with an exception and extra attributes without restructuring your Workers code.
javascript
copy
// In your Worker handler:
const span = getActiveSpan();
span.setAttributes({ 'user.id': '123', 'request.region': 'eu' });
try {
await riskyOperation();
} catch (e) {
recordException(e);
}
Adds ctx.exports access for Workflows declared in the exports field of Wrangler configuration, including in local development.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds getActiveSpan() , recordException() , startSpan() , and setAttributes() APIs to Workers tracing, enabling span creation without changing active context, exception annotation, and bulk attribute setting. Adds document.modelContext API support for WebMCP in Browser Run Kitesurf sessions, testable via the Chrome DevTools WebMCP panel. Adds per-domain email sending suppressions, allowing suppressions to apply to a single sending domain instead of all domains in an account. Workers Metrics charts now display all releases and each traffic allocation change across gradual deployments within the selected time range.
Adds ctx.exports access for Workflows declared in the exports field of Wrangler configuration, including in local development.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds getActiveSpan() , recordException() , startSpan() , and setAttributes() APIs to Workers tracing, enabling span creation without changing active context, exception annotation, and bulk attribute setting.
3 more in Everything
Cloudflare: Supports subscribing to Browser Run crawl lifecycle events via Cloudflare Queues.
└──▷ USE IT
Annotate the current span and record an exception from anywhere inside a Worker handler without needing to thread a span reference through your code.
javascript
copy
import { getActiveSpan, recordException, setAttributes } from 'cloudflare:workers';
export default {
async fetch(request, env, ctx) {
const span = getActiveSpan();
setAttributes({ 'http.method': request.method, 'user.region': request.cf?.country });
try {
return await handleRequest(request, env);
} catch (err) {
recordException(err);
throw err;
}
}
};
Browser Run adds WebMCP to Kitesurf and moves to document.modelContext
Sep 28, 2026
· release notes
Browser Run adds WebMCP support in Kitesurf/Lab sessions via document.modelContext API
WebMCP now works in Kitesurf sessions as well as Lab sessions. Both backends use the document.modelContext API from the WebMCP Community Group draft. AI agents can start Chrome DevTools MCP with the --category-experimental-webmcp flag to add the list_webmcp_tools and execute_webmcp_tool tools. CDP CDP Cisco Discovery Protocol, a Cisco-proprietary Layer 2 protocol that advertises device identity, capabilities, and topology between directly connected Cisco gear, giving cyber tools a passive way to map network infrastructure. WebMCP CDP domain.
4 details in Everything
└──▷ BREAKING ON UPGRADE
! Lab sessions no longer expose navigator.modelContextTesting.
Invalidate cached content instead of purging it
Sep 28, 2026
· release notes
Adds invalidate_cache endpoint and dashboard action to mark cache as stale without re-downloading unchanged assets.
Adds the POST /client/v4/zones/{zone_id}/invalidate_cache API endpoint for programmatic cache invalidation Adds an Invalidate Cache button on the Caching > Configuration dashboard page
2 details in Everything
Cloudflare: New endpoint DELETE /accounts/{account_id}/addressing/address_maps/{address_map_id}/zones/{member_zone_id}︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ BREAKING ON UPGRADE
! Removed endpoint DELETE /accounts/{accountId}/v1/images/{imageId}! Removed endpoint DELETE /accounts/{account_identifier}/custom_pages/assets/{asset_name}! Removed endpoint DELETE /accounts/{account_id}/addressing/address_maps/{address_map_id}/zones/{zone_id}! Removed endpoint DELETE /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules! Removed endpoint DELETE /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings! Removed endpoint DELETE /zones/{zone_identifier}/custom_pages/assets/{asset_name}! Removed endpoint GET /accounts/{accountId}/v1/images! Removed endpoint GET /accounts/{accountId}/v1/images/{imageId}! Removed endpoint GET /accounts/{accountId}/v1/images/{imageId}/blob! Removed endpoint GET /accounts/{accountId}/v2/images! Removed endpoint GET /accounts/{accountId}/zones/{zoneId}/v1/images/flows! Removed endpoint GET /accounts/{account_identifier}/custom_pages! Removed endpoint GET /accounts/{account_identifier}/custom_pages/assets! Removed endpoint GET /accounts/{account_identifier}/custom_pages/assets/{asset_name}! Removed endpoint GET /accounts/{account_identifier}/custom_pages/{identifier}! Removed endpoint GET /accounts/{account_id}/security-center/insights/count! Removed endpoint GET /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules! Removed endpoint GET /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings! Removed endpoint GET /zones/{zone_identifier}/custom_pages! Removed endpoint GET /zones/{zone_identifier}/custom_pages/assets! Removed endpoint GET /zones/{zone_identifier}/custom_pages/assets/{asset_name}! Removed endpoint GET /zones/{zone_identifier}/custom_pages/{identifier}! Removed endpoint PATCH /accounts/{accountId}/v1/images/{imageId}! Removed endpoint PATCH /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings! Removed endpoint POST /accounts/{accountId}/v1/images! Removed endpoint POST /accounts/{accountId}/v2/images/direct_upload! Removed endpoint POST /accounts/{account_identifier}/custom_pages/assets! Removed endpoint POST /accounts/{account_identifier}/custom_pages/preview_tokens! Removed endpoint POST /zones/{zone_identifier}/custom_pages/assets! Removed endpoint POST /zones/{zone_identifier}/custom_pages/preview_tokens! Removed endpoint PUT /accounts/{accountId}/v1/images/{imageId}! Removed endpoint PUT /accounts/{accountId}/zones/{zoneId}/v1/images/flows! Removed endpoint PUT /accounts/{account_identifier}/custom_pages/assets/{asset_name}! Removed endpoint PUT /accounts/{account_identifier}/custom_pages/{identifier}! Removed endpoint PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/zones/{zone_id}! Removed endpoint PUT /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules! Removed endpoint PUT /zones/{zone_identifier}/custom_pages/assets/{asset_name}! Removed endpoint PUT /zones/{zone_identifier}/custom_pages/{identifier}! DELETE /zones/{zone_id}/firewall/waf/overrides/{overrides_id}: response schema changed! DELETE /zones/{zone_id}/rate_limits/{rate_limit_id}: response schema changed! GET /zones/{zone_id}/firewall/waf/overrides: response schema changed! GET /zones/{zone_id}/firewall/waf/overrides/{overrides_id}: response schema changed! GET /zones/{zone_id}/rate_limits: response schema changed! GET /zones/{zone_id}/rate_limits/{rate_limit_id}: response schema changed! GET /zones/{zone_id}/spectrum/analytics/aggregate/current: response schema changed! GET /zones/{zone_id}/spectrum/analytics/events/bytime: response schema changed! GET /zones/{zone_id}/spectrum/analytics/events/summary: response schema changed! POST /zones/{zone_id}/firewall/waf/overrides: response schema changed! POST /zones/{zone_id}/rate_limits: response schema changed! PUT /zones/{zone_id}/firewall/waf/overrides/{overrides_id}: response schema changed! PUT /zones/{zone_id}/rate_limits/{rate_limit_id}: response schema changed! Deprecated endpoint GET /accounts/{account_id}/containers/applications/{application_id}/instances (still works)! Deprecated endpoint GET /accounts/{account_id}/dlp/payload_log (still works)! Deprecated endpoint GET /accounts/{account_id}/images/v1/variants/{variant_id}/flat (still works)! Deprecated endpoint POST /accounts/{account_id}/devices/physical-devices/{device_id}/revoke (still works)! Deprecated endpoint POST /accounts/{account_id}/devices/registrations/revoke (still works)! Deprecated endpoint POST /accounts/{account_id}/devices/registrations/unrevoke (still works)! Deprecated endpoint POST /accounts/{account_id}/email-security/investigate/{investigate_id}/reclassify (still works)! Deprecated endpoint POST /accounts/{account_id}/queues/{queue_id}/messages/preview (still works)! Deprecated endpoint POST /accounts/{account_id}/queues/{queue_id}/messages/preview/ack (still works)! Deprecated endpoint PUT /accounts/{account_id}/devices/settings (still works)! Deprecated endpoint PUT /accounts/{account_id}/dlp/payload_log (still works)
Cloudflare adds Browser Run queue subscriptions, Workers OpenTelemetry OpenTelemetry An open standard and set of tools for collecting traces, metrics and logs from applications. It lets services export observability data without tying instrumentation to one monitoring vendor. MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
└──▷ TRY IT
Subscribe to Browser Run crawl events so a downstream Worker triggers on job completion without polling.
copy
$ npx wrangler queues subscription create my-crawl-events --source browserRun --events crawl.started,crawl.updated,crawl.finished Scope an email suppression to a single sending domain so a bounce on mail.myappexample.com does not block the parent domain.
copy
$ curl https://api.cloudflare.com/client/v4/accounts/$ACCOUNT_ID/email/sending/suppressions \
--header "Authorization: Bearer $CLOUDFLARE_API_TOKEN" \
--header "Content-Type: application/json" \
--data '{"email": "user@example.net", "scope": {"type": "sending_domain", "value": "mail.myappexample.com"}}' Apply a Gateway Network policy only to traffic exiting to the public Internet, leaving tunnel-routed traffic unaffected.
📍 net.offramp.type == internet
Adds wrangler queues subscription create <QUEUE_NAME> --source browserRun --events crawl.started,crawl.updated,crawl.finished to subscribe to Browser Run crawl lifecycle events via Cloudflare Queues, enabling event-driven downstream processing without polling.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds scope field to the Email Sending suppressions API (POST /client/v4/accounts/$ACCOUNT_ID/email/sending/suppressions) with values account and sending_domain, enabling per-domain suppression granularity; scope_type=sending_domain&scope_value=<domain> filters list results. Adds tracing.startSpan(name) , tracing.getActiveSpan() , span.recordException(exception) , and span.setAttributes(attributes) to the Workers custom spans API, expanding OpenTelemetry span instrumentation support. Adds setAttribute() and setAttributes() returning the span object so calls can be chained in Workers tracing. Makes MCP server portals generally available, adding Gateway routing for HTTP logging and DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest. SIEM SIEM Security information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents.
+2 more
show less
Adds Managed Ruleset support for accounts using Unified Routing mode in Cloudflare Advanced Network Firewall. Adds release and gradual deployment annotations to Workers Metrics charts, with hover details showing previous/new versions, rollout duration, and per-step traffic percentage.
Adds wrangler queues subscription create <QUEUE_NAME> --source browserRun --events crawl.started,crawl.updated,crawl.finished to subscribe to Browser Run crawl lifecycle events via Cloudflare Queues, enabling event-driven downstream processing without polling.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Makes MCP server portals generally available, adding Gateway routing for HTTP logging and DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest. SIEM SIEM Security information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents. Adds release and gradual deployment annotations to Workers Metrics charts, with hover details showing previous/new versions, rollout duration, and per-step traffic percentage.
4 more in Everything
API surface changed: +89 endpoints, −36 endpoints, 196 modified, 8 deprecated︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
New endpoint DELETE /accounts/{account_id}/custom_pages/assets/{asset_name}︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New endpoint DELETE /accounts/{account_id}/devices/policy/exclude New endpoint DELETE /accounts/{account_id}/devices/policy/fallback_domains New endpoint DELETE /accounts/{account_id}/devices/policy/{policy_id}/exclude New endpoint DELETE /accounts/{account_id}/devices/policy/{policy_id}/fallback_domains
+95 more
show less
New endpoint DELETE /accounts/{account_id}/workers/observability/issues/groups/{groupId} New endpoint DELETE /accounts/{account_id}/workers/observability/issues/groups/{groupId}/members/{issueId} New endpoint DELETE /accounts/{account_id}/workers/workers/{worker_id}/previews/{preview_id} New endpoint DELETE /accounts/{account_id}/workers/workers/{worker_id}/previews/{preview_id}/deployments/{deployment_id} New endpoint DELETE /zones/{zone_id}/custom_pages/assets/{asset_name} New endpoint DELETE /zones/{zone_id}/observability/tracing/rules New endpoint DELETE /zones/{zone_id}/observability/tracing/settings New endpoint DELETE /zones/{zone_id}/pay-per-use/operators/{operator_id}/price New endpoint GET /accounts/{account_id}/browser-rendering/recording/{session_id} New endpoint GET /accounts/{account_id}/browser-rendering/recording/{session_id}/network New endpoint GET /accounts/{account_id}/builds/workers/{script_tag}/previews New endpoint GET /accounts/{account_id}/builds/workers/{script_tag}/previews/{preview_id} New endpoint GET /accounts/{account_id}/builds/workers/{script_tag}/previews/{preview_id}/builds New endpoint GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/categories New endpoint GET /accounts/{account_id}/containers/applications/{application_id}/instances-v2 New endpoint GET /accounts/{account_id}/custom_pages New endpoint GET /accounts/{account_id}/custom_pages/assets New endpoint GET /accounts/{account_id}/custom_pages/assets/{asset_name} New endpoint GET /accounts/{account_id}/custom_pages/{identifier} New endpoint GET /accounts/{account_id}/managed-defense/vulnerability-discovery/repos New endpoint GET /accounts/{account_id}/managed-defense/vulnerability-discovery/repos/{repo_id} New endpoint GET /accounts/{account_id}/managed-defense/vulnerability-discovery/repos/{repo_id}/scans/{scan_id}/report New endpoint GET /accounts/{account_id}/managed-defense/vulnerability-discovery/scans New endpoint GET /accounts/{account_id}/managed-defense/vulnerability-discovery/scans/{scan_id} New endpoint GET /accounts/{account_id}/managed-defense/vulnerability-discovery/scans/{scan_id}/report New endpoint GET /accounts/{account_id}/pay-per-use/enabled-domains New endpoint GET /accounts/{account_id}/pay-per-use/operator/configuration New endpoint GET /accounts/{account_id}/pay-per-use/proposals New endpoint GET /accounts/{account_id}/pay-per-use/usage-stats New endpoint GET /accounts/{account_id}/registrar/registrations/{domain_name}/transfer-in-status New endpoint GET /accounts/{account_id}/security-center/insights/partner-count New endpoint GET /accounts/{account_id}/workers/workers/{worker_id}/previews New endpoint GET /accounts/{account_id}/workers/workers/{worker_id}/previews/{preview_id} New endpoint GET /accounts/{account_id}/workers/workers/{worker_id}/previews/{preview_id}/deployments New endpoint GET /accounts/{account_id}/workers/workers/{worker_id}/previews/{preview_id}/deployments/{deployment_id} New endpoint GET /zones/{zone_id}/custom_pages New endpoint GET /zones/{zone_id}/custom_pages/assets New endpoint GET /zones/{zone_id}/custom_pages/assets/{asset_name} New endpoint GET /zones/{zone_id}/custom_pages/{identifier} New endpoint GET /zones/{zone_id}/images/v1/flows New endpoint GET /zones/{zone_id}/observability/tracing/rules New endpoint GET /zones/{zone_id}/observability/tracing/settings New endpoint GET /zones/{zone_id}/pay-per-use/can_be_enabled New endpoint GET /zones/{zone_id}/pay-per-use/configuration New endpoint GET /zones/{zone_id}/pay-per-use/operators New endpoint GET /zones/{zone_id}/pay-per-use/usage-stats New endpoint GET /zones/{zone_id}/security-center/insights/partner-count New endpoint PATCH /accounts/{account_id}/builds/workers/{script_tag}/previews/{preview_id} New endpoint PATCH /accounts/{account_id}/devices/physical-devices/{device_id} New endpoint PATCH /accounts/{account_id}/pay-per-use/operator/configuration New endpoint PATCH /accounts/{account_id}/pay-per-use/zones_can_be_enabled New endpoint PATCH /accounts/{account_id}/workers/workers/{worker_id}/previews/{preview_id} New endpoint PATCH /accounts/{account_id}/workers/workers/{worker_id}/previews/{preview_id}/deployments/latest New endpoint PATCH /zones/{zone_id}/observability/tracing/settings New endpoint PATCH /zones/{zone_id}/pay-per-use/configuration New endpoint POST /accounts/{account_id}/ai/websearch New endpoint POST /accounts/{account_id}/builds/workers/{script_tag}/migrate_to_previews New endpoint POST /accounts/{account_id}/builds/workers/{script_tag}/previews/{preview_id}/builds New endpoint POST /accounts/{account_id}/custom_pages/assets New endpoint POST /accounts/{account_id}/custom_pages/preview_tokens New endpoint POST /accounts/{account_id}/devices/override_codes New endpoint POST /accounts/{account_id}/managed-defense/vulnerability-discovery/repos New endpoint POST /accounts/{account_id}/managed-defense/vulnerability-discovery/scans New endpoint POST /accounts/{account_id}/pay-per-use/proposals New endpoint POST /accounts/{account_id}/pay-per-use/usage-reports New endpoint POST /accounts/{account_id}/registrar/domain-transfer-check New endpoint POST /accounts/{account_id}/registrar/registrations/{domain_name}/transfer-in New endpoint POST /accounts/{account_id}/workers/durable_objects/namespaces/{id}/query/v2 New endpoint POST /accounts/{account_id}/workers/observability/issues/groups New endpoint POST /accounts/{account_id}/workers/observability/issues/groups/{groupId}/members New endpoint POST /accounts/{account_id}/workers/workers/{worker_id}/previews New endpoint POST /accounts/{account_id}/workers/workers/{worker_id}/previews/{preview_id}/deployments New endpoint POST /zones/{zone_id}/custom_pages/assets New endpoint POST /zones/{zone_id}/custom_pages/preview_tokens New endpoint POST /zones/{zone_id}/pay-per-use/operators/{operator_id}/price New endpoint PUT /accounts/{account_id}/custom_pages/assets/{asset_name} New endpoint PUT /accounts/{account_id}/custom_pages/{identifier} New endpoint PUT /accounts/{account_id}/pay-per-use/operator/configuration New endpoint PUT /accounts/{account_id}/workers/workers/{worker_id}/previews/{preview_id} New endpoint PUT /organizations/{organization_id}/invites/{member_code} New endpoint PUT /zones/{zone_id}/custom_pages/assets/{asset_name} New endpoint PUT /zones/{zone_id}/custom_pages/{identifier} New endpoint PUT /zones/{zone_id}/images/v1/flows New endpoint PUT /zones/{zone_id}/observability/tracing/rules DELETE /accounts/{account_id}/workers/workers/{worker_id}: param force (query) added GET /accounts/{account_id}/ai-search/instances: param hostname (query) added GET /accounts/{account_id}/ai-search/namespaces/{name}/instances: param hostname (query) added GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles: param tag_category_id (query) added GET /accounts/{account_id}/containers/applications: param page_token (query) added; param per_page (query) added GET /accounts/{account_id}/devices/policies: param profile_type (query) added GET /accounts/{account_id}/gateway/lists/{list_id}/items: param page (query) added; param per_page (query) added GET /accounts/{account_id}/gateway/pacfiles: param page (query) added; param per_page (query) added GET /accounts/{account_id}/workers/observability/issues: param type (query) added GET /analytics/sql/introspection: param include_lex (query) added; param include_wae (query) added PATCH /accounts/{account_id}/builds/workers/{script_tag}: param patch_existing_previews (query) added
100 details in Everything
└──▷ BREAKING ON UPGRADE
! Removed endpoint DELETE /accounts/{accountId}/v1/images/{imageId}! Removed endpoint DELETE /accounts/{account_identifier}/custom_pages/assets/{asset_name}! Removed endpoint DELETE /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules! Removed endpoint DELETE /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings! Removed endpoint DELETE /zones/{zone_identifier}/custom_pages/assets/{asset_name}! Removed endpoint GET /accounts/{accountId}/v1/images! Removed endpoint GET /accounts/{accountId}/v1/images/{imageId}! Removed endpoint GET /accounts/{accountId}/v1/images/{imageId}/blob! Removed endpoint GET /accounts/{accountId}/v2/images! Removed endpoint GET /accounts/{accountId}/zones/{zoneId}/v1/images/flows! Removed endpoint GET /accounts/{account_identifier}/custom_pages! Removed endpoint GET /accounts/{account_identifier}/custom_pages/assets! Removed endpoint GET /accounts/{account_identifier}/custom_pages/assets/{asset_name}! Removed endpoint GET /accounts/{account_identifier}/custom_pages/{identifier}! Removed endpoint GET /accounts/{account_id}/security-center/insights/count! Removed endpoint GET /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules! Removed endpoint GET /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings! Removed endpoint GET /zones/{zone_identifier}/custom_pages! Removed endpoint GET /zones/{zone_identifier}/custom_pages/assets! Removed endpoint GET /zones/{zone_identifier}/custom_pages/assets/{asset_name}! Removed endpoint GET /zones/{zone_identifier}/custom_pages/{identifier}! Removed endpoint PATCH /accounts/{accountId}/v1/images/{imageId}! Removed endpoint PATCH /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings! Removed endpoint POST /accounts/{accountId}/v1/images! Removed endpoint POST /accounts/{accountId}/v2/images/direct_upload! Removed endpoint POST /accounts/{account_identifier}/custom_pages/assets! Removed endpoint POST /accounts/{account_identifier}/custom_pages/preview_tokens! Removed endpoint POST /zones/{zone_identifier}/custom_pages/assets! Removed endpoint POST /zones/{zone_identifier}/custom_pages/preview_tokens! Removed endpoint PUT /accounts/{accountId}/v1/images/{imageId}! Removed endpoint PUT /accounts/{accountId}/zones/{zoneId}/v1/images/flows! Removed endpoint PUT /accounts/{account_identifier}/custom_pages/assets/{asset_name}! Removed endpoint PUT /accounts/{account_identifier}/custom_pages/{identifier}! Removed endpoint PUT /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules! Removed endpoint PUT /zones/{zone_identifier}/custom_pages/assets/{asset_name}! Removed endpoint PUT /zones/{zone_identifier}/custom_pages/{identifier}! DELETE /zones/{zone_id}/firewall/waf/overrides/{overrides_id}: response schema changed! DELETE /zones/{zone_id}/rate_limits/{rate_limit_id}: response schema changed! GET /zones/{zone_id}/firewall/waf/overrides: response schema changed! GET /zones/{zone_id}/firewall/waf/overrides/{overrides_id}: response schema changed! GET /zones/{zone_id}/rate_limits: response schema changed! GET /zones/{zone_id}/rate_limits/{rate_limit_id}: response schema changed! GET /zones/{zone_id}/spectrum/analytics/aggregate/current: response schema changed! GET /zones/{zone_id}/spectrum/analytics/events/bytime: response schema changed! GET /zones/{zone_id}/spectrum/analytics/events/summary: response schema changed! POST /zones/{zone_id}/firewall/waf/overrides: response schema changed! POST /zones/{zone_id}/rate_limits: response schema changed! PUT /zones/{zone_id}/firewall/waf/overrides/{overrides_id}: response schema changed! PUT /zones/{zone_id}/rate_limits/{rate_limit_id}: response schema changed! Deprecated endpoint GET /accounts/{account_id}/containers/applications/{application_id}/instances (still works)! Deprecated endpoint GET /accounts/{account_id}/images/v1/variants/{variant_id}/flat (still works)! Deprecated endpoint POST /accounts/{account_id}/devices/physical-devices/{device_id}/revoke (still works)! Deprecated endpoint POST /accounts/{account_id}/devices/registrations/revoke (still works)! Deprecated endpoint POST /accounts/{account_id}/devices/registrations/unrevoke (still works)! Deprecated endpoint POST /accounts/{account_id}/queues/{queue_id}/messages/preview (still works)! Deprecated endpoint POST /accounts/{account_id}/queues/{queue_id}/messages/preview/ack (still works)! Deprecated endpoint PUT /accounts/{account_id}/devices/settings (still works)
Cloudflare Workers AI adds claude-opus-5.5, gpt-6-luna, gpt-6-sol, and grok-4.7 to its model catalog.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds claude-opus-5.5 (Anthropic Claude Opus 5.5) with a 1 million token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. Adds gpt-6-luna (OpenAI GPT-6 Luna), the most efficient GPT-6 variant, optimized for focused, high-volume tasks. Adds gpt-6-sol (OpenAI GPT-6 Sol), the mid-tier GPT-6 variant, built for complex coding and agentic workflows. Adds grok-4.7 (xAI), a frontier reasoning model supporting text and image inputs, function calling function calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions. structured outputs structured outputs Forcing a model's response to match a given format or JSON schema, so software can parse it reliably instead of hoping the text is well formed. low, medium, high, xhigh).
4 details in Everything
└──▷ USE IT
Apply a Gateway HTTP policy only to traffic destined for the public Internet, leaving traffic routed through Cloudflare Tunnel untouched.
env
copy
net.offramp.type == "internet"
Verify that 1.1.1.1 trusts the KSK-2024 DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit.
copy
$ dig @1.1.1.1 root-key-sentinel-is-ta-38696.dnstest.dev. +noall +comments +answer Build a rich origin context header using up to 32 concat() arguments in a Rulesets API Request Header Transform Rule.
copy
$ curl -s -X POST "https://api.cloudflare.com/client/v4/zones/$ZONE_ID/rulesets/$RULESET_ID/rules" \
-H "Authorization: Bearer $API_TOKEN" \
-H "Content-Type: application/json" \
-d '{
"ref": "add_request_context_header",
"description": "Add request context for the origin",
"expression": "true",
"action": "rewrite",
"action_parameters": {
"headers": {
"X-Request-Context": {
"operation": "set",
"expression": "concat(\"ip=\", to_string(ip.src), \";country=\", ip.src.country, \";host=\", http.host, \";method=\", http.request.method, \";path=\", http.request.uri.path, \";ray-id=\", cf.ray_id, \";asn=\", to_string(ip.src.asnum), \";user-agent=\", http.user_agent)"
}
}
}
}'
Cloudflare: Adds AI Search instance create and update endpoints, with notes that Search for Agents requires the default namespace.
└──▷ TRY IT
Retrieve the current tracing settings for a zone to verify observability configuration before making changes.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/zones/{zone_id}/observability/tracing/settings' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' Restart a Hyperdrive config after updating connection pool or caching parameters to apply changes without recreating the resource.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/{account_id}/hyperdrive/configs/{hyperdrive_id}/restart' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json'
Bumps the cloudflare-go SDK to v7.11.0 (go get -u github.com/cloudflare/cloudflare-go/v7@v7.11.0).
1 more in Everything
Cloudflare: MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
└──▷ HOW TO FIND IT
When you want a Gateway Network policy to match only traffic that exits via a specific destination type, use the new Traffic Destination selector to target that exit path.
📍 In the Cloudflare Zero Trust dashboard, go to Gateway › Policies › Network (or HTTP), create or edit a policy, add a selector, and choose Traffic Destination to match traffic based on how it exits Cloudflare.
1.1.1.1 now supports RFC 8509 RFC 8509 An IETF standards document specifying a mechanism for DNS resolvers to signal which root key signing keys they trust, letting operators detect mismatches during DNSSEC root key rollovers. DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit. Adds account-level transformation analytics for Cloudflare Images usage. Adds guided onboarding for Mesh participants, including node deployment setup, client installers, organization name lookup, and a unified participant management table.
3 details in Everything
└──▷ HOW TO FIND IT
Route Gateway Network policy decisions based on egress path — for example, block traffic that exits via a specific egress location.
📍 In the Cloudflare Zero Trust dashboard, go to Gateway › Policies › Network, create or edit a policy, add a selector, and choose Traffic Destination to match on how traffic exits Cloudflare.
Cloudflare: Adds Logpush support for MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. SIEM SIEM Security information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents.
└──▷ TRY IT
Deploy a Worker Preview for an in-progress branch so reviewers can test against an isolated, production-like environment before merging.
copy
$ npx wrangler preview
Adds Static OAuth client credentials support to MCP server portals for providers that do not support Dynamic Client Registration. Adds Service token authentication to MCP server portals for autonomous agents and machine-to-machine access. Adds Code Mode policies to MCP server portals to control how portals reduce tool definitions and token use. MCP server portals are now generally available to all Cloudflare customers, providing a single endpoint for approved Model Context Protocol Model Context Protocol Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Adds a product-level Metrics page to the Cloudflare dashboard for R2, showing bandwidth usage split by object upload and download across all buckets or per bucket, also exposed via the GraphQL Analytics API.
+5 more
show less
Adds Worker Previews, giving each pull request an isolated, production-like environment with its own code, configuration, URL, logs, errors, metrics, and traces. Durable Object name search in the Cloudflare dashboard now accepts up to 128 characters, up from 20, applying to the Metrics tab object filter and Data Studio object search. 1.1.1.1 adds RFC 8509 RFC 8509 An IETF standards document specifying a mechanism for DNS resolvers to signal which root key signing keys they trust, letting operators detect mismatches during DNSSEC root key rollovers. root-key-sentinel-is-ta-38696.dnstest.dev) to verify whether the resolver trusts a DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit. Adds Gateway routing to MCP server portals for HTTP logging and data loss prevention (DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest. Adds Session management to MCP server portals for reconnecting servers and changing authorizations from the portal.
MCP server portals are now generally available to all Cloudflare customers, providing a single endpoint for approved Model Context Protocol Model Context Protocol Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Adds a product-level Metrics page to the Cloudflare dashboard for R2, showing bandwidth usage split by object upload and download across all buckets or per bucket, also exposed via the GraphQL Analytics API. Adds Worker Previews, giving each pull request an isolated, production-like environment with its own code, configuration, URL, logs, errors, metrics, and traces. 1.1.1.1 adds RFC 8509 RFC 8509 An IETF standards document specifying a mechanism for DNS resolvers to signal which root key signing keys they trust, letting operators detect mismatches during DNSSEC root key rollovers. root-key-sentinel-is-ta-38696.dnstest.dev) to verify whether the resolver trusts a DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit.
6 more in Everything
Managed Rulesets supported in Unified Routing
Sep 25, 2026
· release notes
Managed Rulesets now supported in Unified Routing mode
Workers tracing — new getActiveSpan(), recordException(), startSpan(), and setAttributes() APIs
Sep 25, 2026
· release notes
Cloudflare Workers adds getActiveSpan() , startSpan() , recordException() , and setAttributes() to tracing API
tracing.startSpan(name) creates a span that does not become the active span and returns it directly.tracing.getActiveSpan() returns the currently active span, or the root span outside any custom spans, enabling annotation from helpers without passing objects.span.recordException(exception) records an exception event on a specific span, accepting an Error, string, or object with code/name/message.span.setAttributes(attributes) and span.setAttribute() now return the span instance, allowing method chaining.
4 details in Everything
Suppress recipients for one sending domain
Sep 25, 2026
· release notes
Cloudflare Email Sending now supports sending-domain-level recipient suppressions via API and dashboard.
Adds scope parameter to the Email Sending suppressions API endpoint for granular suppression targeting Enables filtering suppressions by scope_type and scope_value query parameters in the GET /email/sending/suppressions API Adds Sending domain option to the Scope dropdown in the Email Sending > Suppressions dashboard UI
3 details in Everything
See every release and gradual deployment on Workers Metrics charts
Sep 25, 2026
· release notes
Workers Metrics charts now show every release and gradual deployment rollout as annotations
Cloudflare: Introduces Worker Previews, letting each pull request run in an isolated environment with its own code, URL, bindings, logs, metrics, and traces, configured via the previews block in the Wrangler configuration file and deployed with npx wrangler preview (requires Wrangler 4.135.0 or later).
└──▷ TRY IT
Write a Gateway Network policy that applies stricter controls only to traffic leaving via Cloudflare Tunnel, while letting public Internet traffic follow a separate rule.
copy
$ # In the Cloudflare dashboard or via the Zero Trust API, add a Network policy condition:
# Selector: Traffic Destination | Operator: is | Value: cloudflare_tunnel
# API field equivalent:
net.offramp.type == "cloudflare_tunnel" Deploy a Worker Preview for a feature branch so reviewers get an isolated, production-like URL without affecting production or other previews.
copy
$ npx wrangler preview Add a 32-argument concat() header-rewrite rule to bundle request context into a single origin header, using the Rulesets API on the http_request_late_transform phase.
copy
$ curl --request POST \
"https://api.cloudflare.com/client/v4/zones/$ZONE_ID/rulesets/$RULESET_ID/rules" \
--header "Authorization: Bearer $CLOUDFLARE_API_TOKEN" \
--header "Content-Type: application/json" \
--data '{
"ref": "add_request_context_header",
"description": "Add request context for the origin",
"expression": "true",
"action": "rewrite",
"action_parameters": {
"headers": {
"X-Request-Context": {
"operation": "set",
"expression": "concat(\"ip=\", to_string(ip.src), \";country=\", ip.src.country, \";host=\", http.host, \";method=\", http.request.method, \";path=\", http.request.uri.path, \";query=\", http.request.uri.query, \";ray-id=\", cf.ray_id, \";asn=\", to_string(ip.src.asnum), \";user-agent=\", http.user_agent)"
}
}
}
}'
Introduces account-level transformation analytics in Images, showing request traffic split by URL-based vs. Images binding transformations, top zones, configurations, origin hosts, and Worker scripts.
1 detail in Everything
Cloudflare adds Traffic Destination selector, Worker Previews, private MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
└──▷ USE IT
Apply a stricter Gateway HTTP policy only to traffic headed for the public Internet, leaving tunnel-routed traffic under a different rule set.
text
copy
# In a Gateway HTTP policy expression:
net.offramp.type == "internet"
Deploy a Worker Preview for a feature branch so reviewers get an isolated, production-like URL without touching production.
copy
$ npx wrangler preview Route browser-binding requests for an internal hostname through an outbound Worker that adds auth, instead of exposing the service publicly.
javascript
copy
const connection = await BROWSER.acquire({
outboundByHost: {
"private.example.test": env.OUTBOUND
}
});
const session = await BROWSER.connectSession(sessionId);
Adds net.offramp.type API field as the Traffic Destination selector in Gateway HTTP and Network policies, with values internet, cloudflare_wan, cloudflare_tunnel, device_client, and mesh to target specific off-ramp methods.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds acquire() and launch() methods to browser bindings with an outboundByHost option to route per-hostname requests through another Worker, plus connectSession(sessionId) and a nested devtools binding for typed DevTools and session-management operations. Adds guided onboarding for Cloudflare Mesh participants from the dashboard, with deployment options for Linux, Kubernetes, Docker Compose, and Docker CLI, plus a unified node-and-device management table.
Adds net.offramp.type API field as the Traffic Destination selector in Gateway HTTP and Network policies, with values internet, cloudflare_wan, cloudflare_tunnel, device_client, and mesh to target specific off-ramp methods.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds acquire() and launch() methods to browser bindings with an outboundByHost option to route per-hostname requests through another Worker, plus connectSession(sessionId) and a nested devtools binding for typed DevTools and session-management operations.
1 more in Everything
New R2 Metrics page and GraphQL Analytics API for bandwidth usage
Adds R2 Metrics dashboard page to view bucket-level bandwidth throughput split by upload and download
1 detail in Everything
MCP server portals are now generally available
Sep 24, 2026
· release notes
Cloudflare makes MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds Gateway routing for HTTP logging and data loss prevention (DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest. Adds Code Mode policies that control how portals reduce tool definitions and token use Adds Static OAuth client credentials for providers that do not support Dynamic Client Registration Adds Session management for reconnecting servers and changing authorizations from the portal Adds Service token authentication for autonomous agents and machine-to-machine access
+1 more
show less
Adds Logpush support for exporting portal activity to external storage or a security information and event management security information and event management Security information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents. SIEM SIEM Security information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents.
6 details in Everything
RFC 8509 root key trust anchor sentinel support
Sep 24, 2026
· release notes
1.1.1.1 adds RFC 8509 RFC 8509 An IETF standards document specifying a mechanism for DNS resolvers to signal which root key signing keys they trust, letting operators detect mismatches during DNSSEC root key rollovers. DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit.
Adds root-key-sentinel-is-ta-<keytag>.dnstest.dev and root-key-sentinel-not-ta-<keytag>.dnstest.dev domain queries to check whether 1.1.1.1 trusts a specific DNSSEC root key ahead of rollover
1 detail in Everything
Declare Workflows in the `exports` configuration
Sep 24, 2026
· release notes
Workers now allow declaring Workflow exports in wrangler.toml via the exports field
Adds exports configuration key support for defining Worker-bound Workflows in wrangler.toml Enables declaration of Workflow limits (e.g., limits.steps) and schedules directly in wrangler.toml exports
2 details in Everything
Cloudflare adds Worker Previews, private MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Rulesets Rulesets Named collections of detection or filtering logic—conditions, signatures, or policies—that a cyber tool evaluates against data to decide what to flag, block, or allow. DDoS DDoS Distributed Denial of Service: an attack that floods a target system with traffic from many sources simultaneously, exhausting its resources so legitimate requests cannot be served.
└──▷ TRY IT
Validate a new custom firewall ruleset against Cloudflare's server-side checks before publishing it, catching expression or quota errors without making any live changes.
copy
$ curl -s -X POST "https://api.cloudflare.com/client/v4/zones/$ZONE_ID/rulesets?dry_run=true" \
-H "Authorization: Bearer $CF_API_TOKEN" \
-H "Content-Type: application/json" \
-d '{
"name": "Custom firewall rules",
"kind": "zone",
"phase": "http_request_firewall_custom",
"rules": [
{
"action": "block",
"expression": "ip.src.country eq \"GB\"",
"description": "Block requests from GB"
}
]
}' Define an isolated Worker Preview environment with its own D1 binding so that CI pull-request tests never touch the production database.
wrangler.toml
copy
[[previews]]
name = "pr-preview"
[[previews.d1_databases]]
binding = "DB"
database_id = "<preview-database-id>"
Adds dry_run=true query parameter to Rulesets API mutation endpoints to validate ruleset changes — expressions, action parameters, permissions, and quota limits — without persisting or publishing them; successful no-op operations return result: null.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds filter_attack_traffic field to Logpush job API requests to exclude identified DDoS attack traffic from delivered logs, supporting http_requests, firewall_events, and network_analytics_logs datasets; also available in the dashboard under Exclude DDoS attack traffic in Advanced Options. Adds acquire() and launch() browser binding methods that accept outboundByHost to route requests for selected hostnames through another Worker, enabling access to private services or adding authentication without constructing raw HTTP requests. Adds connectSession(sessionId) browser binding method that returns a session-pinned webSocket Fetcher for a CDP CDP Cisco Discovery Protocol, a Cisco-proprietary Layer 2 protocol that advertises device identity, capabilities, and topology between directly connected Cisco gear, giving cyber tools a passive way to map network infrastructure. devtools binding with typed methods for browser version info, protocol descriptions, and target operations (list, create, activate, close). Adds previews block to Wrangler configuration file to define variables, bindings, and settings for Worker Previews — isolated, production-like environments with their own code, URLs, and observability; requires Wrangler 4.135.0 or later to deploy with wrangler deploy --preview.
+7 more
show less
Supports Workers Builds integration with Cursor Origin repositories to automatically build and deploy Workers, generate preview URLs for non-production branches, and post build status and check runs to Cursor Origin pull requests. Adds automatic inactive service token management for Cloudflare Access, with a configurable inactivity period of 30 to 365 days and the choice to disable or delete tokens that have not authenticated and are not referenced by an Access policy rule. Adds private MCP server support to MCP server portals via Cloudflare Gateway, allowing portals to reach private hostnames and IP addresses without exposing the MCP server to the public Internet; enabled by toggling Route traffic through Cloudflare Gateway when adding the server. Expands the concat() function in Cloudflare Rules to accept up to 32 arguments, up from 16, for building richer dynamic values in Rules expressions. Adds new WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. SSTI SSTI Server-Side Template Injection, a vulnerability class where attacker-controlled input is evaluated by a server-side template engine, enabling remote code execution or data exfiltration. Adds Windows service recovery mechanism backed by a Windows scheduler task to restart the WARP service on system unlock if it is not already running. Removes the requirement for the Windows WLAN AutoConfig service to be running for the Cloudflare One Client on Windows.
Adds dry_run=true query parameter to Rulesets API mutation endpoints to validate ruleset changes — expressions, action parameters, permissions, and quota limits — without persisting or publishing them; successful no-op operations return result: null.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds filter_attack_traffic field to Logpush job API requests to exclude identified DDoS attack traffic from delivered logs, supporting http_requests, firewall_events, and network_analytics_logs datasets; also available in the dashboard under Exclude DDoS attack traffic in Advanced Options. Adds connectSession(sessionId) browser binding method that returns a session-pinned webSocket Fetcher for a CDP CDP Cisco Discovery Protocol, a Cisco-proprietary Layer 2 protocol that advertises device identity, capabilities, and topology between directly connected Cisco gear, giving cyber tools a passive way to map network infrastructure. devtools binding with typed methods for browser version info, protocol descriptions, and target operations (list, create, activate, close). Adds previews block to Wrangler configuration file to define variables, bindings, and settings for Worker Previews — isolated, production-like environments with their own code, URLs, and observability; requires Wrangler 4.135.0 or later to deploy with wrangler deploy --preview. Supports Workers Builds integration with Cursor Origin repositories to automatically build and deploy Workers, generate preview URLs for non-production branches, and post build status and check runs to Cursor Origin pull requests.
+4 more
show less
Adds automatic inactive service token management for Cloudflare Access, with a configurable inactivity period of 30 to 365 days and the choice to disable or delete tokens that have not authenticated and are not referenced by an Access policy rule. Adds private MCP server support to MCP server portals via Cloudflare Gateway, allowing portals to reach private hostnames and IP addresses without exposing the MCP server to the public Internet; enabled by toggling Route traffic through Cloudflare Gateway when adding the server. Adds new WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. SSTI SSTI Server-Side Template Injection, a vulnerability class where attacker-controlled input is evaluated by a server-side template engine, enabling remote code execution or data exfiltration. Adds Windows service recovery mechanism backed by a Windows scheduler task to restart the WARP service on system unlock if it is not already running.
3 more in Everything
Cloudflare API adds zone tracing, posture rules, SFU SFU A Selective Forwarding Unit: a media server architecture that relays incoming WebRTC streams to other participants without decoding them, reducing server CPU cost and latency in multi-party video or data pipelines.
└──▷ TRY IT
Enable and inspect per-zone request tracing to diagnose how traffic flows through Cloudflare rules and Workers.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/zones/{zone_id}/observability/tracing/settings' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' Restart a Hyperdrive config after updating connection pool credentials to pick up new settings without recreation.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/{account_id}/hyperdrive/configs/{hyperdrive_id}/restart' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' Grant a sub-account membership to an Address Map so that account can route traffic through the shared IP block.
copy
$ curl -X PUT 'https://api.cloudflare.com/client/v4/accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{member_account_id}' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json'
Adds GET/PUT/DELETE /zones/{zone_id}/observability/tracing/settings endpoints to view, update, and reset per-zone tracing settings.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds GET/PUT/DELETE /zones/{zone_id}/observability/tracing/rules endpoints to view, replace, and delete zone trace rules. Adds PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{member_account_id} and DELETE on the same path to add or remove an account membership from an Address Map. Adds GET and PUT endpoints for device settings, plus a reset device settings endpoint. Adds Global Disconnect endpoints (GET and SET) for device management.
+2 more
show less
Adds POST /accounts/{account_id}/hyperdrive/configs/{hyperdrive_id}/restart endpoint to restart a Hyperdrive configuration. Adds TURN key management endpoints: list, create, and update TURN key details.
7 details in Everything
Cloudflare adds inactive token lifecycle management, private MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. concat() , Cursor Origin builds, and per-PR Worker Previews.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ USE IT
Build a dynamic hostname header in a Rules expression by combining multiple values — now up to 32 — with concat() .
text
copy
concat(http.host, "-", cf.ray_id, "-", ip.src, "-", http.request.uri.path)
Adds concat() support for up to 32 arguments in Rules expressions, enabling richer dynamic value construction.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds private network MCP server support for MCP server portals, allowing portals to connect to MCP servers available only on a private network. Adds Cursor Origin repository support in Workers Builds for automatic deployments, branch previews, and build status reporting. Adds Worker Previews, giving every pull request its own URL, configuration, observability, and isolated Durable Objects and Containers.
Adds concat() support for up to 32 arguments in Rules expressions, enabling richer dynamic value construction.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Worker Previews, giving every pull request its own URL, configuration, observability, and isolated Durable Objects and Containers.
2 more in Everything
View transformation analytics in Images
Sep 23, 2026
· release notes
New UI view for account-level Images transformation analytics in Cloudflare dashboard
Adds a new Transformations > Analytics view in the Cloudflare console to monitor image transformation request traffic.
1 detail in Everything
Add Mesh participants with guided onboarding
Sep 23, 2026
· release notes
Cloudflare Mesh dashboard adds guided onboarding for participants with unified management and multi-platform deployment guidance.
Adds Add participant action in Networking > Mesh to deploy a Mesh node or connect a client device Supports Mesh node installation on Linux, Kubernetes, Docker Compose, and Docker CLI via dashboard requirements and commands Provides platform-specific Cloudflare One Client installers, mobile QR codes, and organization name for client logins Unified participant table shows Mesh nodes and enrolled client devices with search, filter by type/status, and source retry logic
4 details in Everything
Traffic Destination selector in Gateway policies
Sep 23, 2026
· release notes
Adds Traffic Destination selector (net.offramp.type) to Gateway HTTP and Network policies for targeting specific off-ramps
Supports targeting five specific traffic destination values: internet, cloudflare_wan, cloudflare_tunnel, device_client, and mesh via the net.offramp.type API field.
1 detail in Everything
Durable Object name search now supports 128 characters
Sep 23, 2026
· release notes
Durable Object name search limit raised from 20 to 128 characters
Metrics tab object filter and Data Studio object search now accept Durable Object names up to 128 characters long.
1 detail in Everything
WAF - WAF Release - 2026-09-22 (2026-09-22)
Sep 22, 2026
·
issue 083
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. SSTI SSTI Server-Side Template Injection, a vulnerability class where attacker-controlled input is evaluated by a server-side template engine, enabling remote code execution or data exfiltration.
Adds managed rule ...5f21b651 to block SSRF attempts using cloud and link-local non-standard IP notation (action changed from Log to Block).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds managed rule ...0f0313d6 to block SSRF attempts using jar HTTP loopback payloads (action changed from Log to Block). Adds managed rule ...75cd912a to block SSRF attempts using local non-standard IP notation (action changed from Log to Block). Adds managed rule ...a1ba83f6 to block Server-Side Template Injection targeting Jinja Dangerous Globals chains (action changed from Log to Block).
4 details in Everything
concat() now supports up to 32 arguments
Sep 22, 2026
· release notes
Cloudflare Ruleset concat() function argument limit increased from 16 to 32.
concat() in Cloudflare Rules now supports up to 32 arguments, enabling richer dynamic value construction within Rules expressions.
1 detail in Everything
New WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. SSTI SSTI Server-Side Template Injection, a vulnerability class where attacker-controlled input is evaluated by a server-side template engine, enabling remote code execution or data exfiltration.
Changes detection for SSRF - Cloud,Link-Local non-standard IP notation from Log to Block Changes detection for 'SSRF - Block jar HTTP loopback payload' from Log to Block Changes detection for SSRF - Local non-standard IP notation from Log to Block Adds new rule ID ...a1ba83f6 for SSTI - Jinja Dangerous Globals Chain with Block action
4 details in Everything
Automatically manage inactive Access service tokens
Sep 22, 2026
· release notes
Cloudflare Access can now automatically disable or delete inactive service tokens via configurable cleanup policies.
Enables automatic management of inactive Access service tokens for administrators Allows setting an inactivity period from 30 to 365 days for token eligibility Supports choosing between disabling or deleting tokens that reach the configured limit
3 details in Everything
Test every pull request in an isolated environment with Worker Previews
Sep 22, 2026
· release notes
Worker Previews allows isolated testing of pull requests with Wrangler CLI and Workers Builds integration
└──▷ TRY IT
Deploy a local worker change for immediate testing in an isolated environment
copy
$ npx wrangler preview
Adds wrangler preview subcommand to deploy and test Worker changes in an isolated environment Adds previews block to Wrangler configuration file to define default variables, bindings, and settings for new previews Enables Workers Builds integration to automatically create preview URLs and post them to pull requests
3 details in Everything
Private MCP server support for MCP server portals
Sep 22, 2026
· release notes
Add private network support for MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
MCP server portals can now connect to MCP servers available only on your private network by routing through Cloudflare Gateway. The new workflow supports connecting the server network using Cloudflare Tunnel, Cloudflare Mesh, or another Cloudflare One connector without exposing the MCP server to the public Internet.
2 details in Everything
API surface changed: +14 endpoints, 22 modified, 13 deprecated︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
API change API surface changed: +14 endpoints, 22 modified, 13 deprecated︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
+ DELETE /accounts/{account_id}/workers/observability/issues/automations/{automationId} + DELETE /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules + DELETE /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings + GET /accounts/{account_id}/billable/usage/billable-metrics + GET /accounts/{account_id}/workers/observability/issues + GET /accounts/{account_id}/workers/observability/issues/automations + GET /accounts/{account_id}/workers/observability/issues/automations/{automationId} + GET /accounts/{account_id}/workers/observability/issues/summary + GET /accounts/{account_id}/workers/observability/issues/{issueId} + GET /accounts/{account_id}/workers/observability/issues/{issueId}/occurrences + PATCH /accounts/{account_id}/workers/observability/issues/{issueId} + POST /accounts/{account_id}/workers/observability/issues/automations + POST /accounts/{account_id}/workers/observability/issues/{issueId}/notification-runs + PUT /accounts/{account_id}/workers/observability/issues/automations/{automationId}
~ GET /accounts/{account_identifier}/custom_pages: response schema changed ~ GET /accounts/{account_identifier}/custom_pages/assets: response schema changed ~ GET /accounts/{account_identifier}/custom_pages/assets/{asset_name}: response schema changed ~ GET /accounts/{account_identifier}/custom_pages/{identifier}: response schema changed ~ GET /accounts/{account_id}/workers/scripts/{script_name}/deployments: param page (query) added; param per_page (query) added; param since (query) added; param until (query) added ~ GET /analytics/sql/introspection: param include_custom_attributes (query) added; response schema changed ~ GET /zones/{zone_identifier}/custom_pages: response schema changed ~ GET /zones/{zone_identifier}/custom_pages/assets: response schema changed ~ GET /zones/{zone_identifier}/custom_pages/assets/{asset_name}: response schema changed ~ GET /zones/{zone_identifier}/custom_pages/{identifier}: response schema changed ~ PATCH /accounts/{account_id}/containers/applications/{application_id}: request body changed ~ POST /accounts/{account_identifier}/custom_pages/assets: response schema changed ~ POST /accounts/{account_identifier}/custom_pages/preview_tokens: response schema changed ~ POST /accounts/{account_id}/data-security/posture/webhooks: request body changed ~ POST /accounts/{account_id}/email/sending/send: response schema changed ~ POST /accounts/{account_id}/email/sending/send_raw: response schema changed ~ POST /zones/{zone_identifier}/custom_pages/assets: response schema changed ~ POST /zones/{zone_identifier}/custom_pages/preview_tokens: response schema changed ~ PUT /accounts/{account_identifier}/custom_pages/assets/{asset_name}: response schema changed ~ PUT /accounts/{account_identifier}/custom_pages/{identifier}: response schema changed ~ PUT /zones/{zone_identifier}/custom_pages/assets/{asset_name}: response schema changed ~ PUT /zones/{zone_identifier}/custom_pages/{identifier}: response schema changed
⚠ DELETE /accounts/{account_id}/ai-search/instances/{id} ⚠ GET /accounts/{account_id}/ai-search/instances ⚠ GET /accounts/{account_id}/ai-search/instances/{id} ⚠ GET /accounts/{account_id}/ai-search/instances/{id}/jobs ⚠ GET /accounts/{account_id}/ai-search/instances/{id}/jobs/{job_id} ⚠ GET /accounts/{account_id}/ai-search/instances/{id}/jobs/{job_id}/logs ⚠ GET /accounts/{account_id}/ai-search/instances/{id}/stats ⚠ PATCH /accounts/{account_id}/ai-search/instances/{id}/jobs/{job_id} ⚠ POST /accounts/{account_id}/ai-search/instances ⚠ POST /accounts/{account_id}/ai-search/instances/{id}/chat/completions ⚠ POST /accounts/{account_id}/ai-search/instances/{id}/jobs ⚠ POST /accounts/{account_id}/ai-search/instances/{id}/search ⚠ PUT /accounts/{account_id}/ai-search/instances/{id}
New endpoint DELETE /accounts/{account_id}/workers/observability/issues/automations/{automationId}︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New endpoint DELETE /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules New endpoint DELETE /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings New endpoint GET /accounts/{account_id}/billable/usage/billable-metrics New endpoint GET /accounts/{account_id}/workers/observability/issues
+11 more
show less
New endpoint GET /accounts/{account_id}/workers/observability/issues/automations New endpoint GET /accounts/{account_id}/workers/observability/issues/automations/{automationId} New endpoint GET /accounts/{account_id}/workers/observability/issues/summary New endpoint GET /accounts/{account_id}/workers/observability/issues/{issueId} New endpoint GET /accounts/{account_id}/workers/observability/issues/{issueId}/occurrences New endpoint PATCH /accounts/{account_id}/workers/observability/issues/{issueId} New endpoint POST /accounts/{account_id}/workers/observability/issues/automations New endpoint POST /accounts/{account_id}/workers/observability/issues/{issueId}/notification-runs New endpoint PUT /accounts/{account_id}/workers/observability/issues/automations/{automationId} GET /accounts/{account_id}/workers/scripts/{script_name}/deployments: param page (query) added; param per_page (query) added; param since (query) added; param until (query) added GET /analytics/sql/introspection: param include_custom_attributes (query) added
16 details in Everything
└──▷ BREAKING ON UPGRADE
! Deprecated endpoint DELETE /accounts/{account_id}/ai-search/instances/{id} (still works)! Deprecated endpoint GET /accounts/{account_id}/ai-search/instances (still works)! Deprecated endpoint GET /accounts/{account_id}/ai-search/instances/{id} (still works)! Deprecated endpoint GET /accounts/{account_id}/ai-search/instances/{id}/jobs (still works)! Deprecated endpoint GET /accounts/{account_id}/ai-search/instances/{id}/jobs/{job_id} (still works)! Deprecated endpoint GET /accounts/{account_id}/ai-search/instances/{id}/jobs/{job_id}/logs (still works)! Deprecated endpoint GET /accounts/{account_id}/ai-search/instances/{id}/stats (still works)! Deprecated endpoint PATCH /accounts/{account_id}/ai-search/instances/{id}/jobs/{job_id} (still works)! Deprecated endpoint POST /accounts/{account_id}/ai-search/instances (still works)! Deprecated endpoint POST /accounts/{account_id}/ai-search/instances/{id}/chat/completions (still works)! Deprecated endpoint POST /accounts/{account_id}/ai-search/instances/{id}/jobs (still works)! Deprecated endpoint POST /accounts/{account_id}/ai-search/instances/{id}/search (still works)! Deprecated endpoint PUT /accounts/{account_id}/ai-search/instances/{id} (still works)
Cloudflare Workers AI adds 14+ new models including video generation, multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats.
└──▷ TRY IT
Generate a 1080P cinematic video from a text prompt using the new wan-3.0-prime model via the Workers AI REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
copy
$ curl https://api.cloudflare.com/client/v4/accounts/<ACCOUNT_ID>/ai/run/@cf/alibaba/wan-3.0-prime -H 'Authorization: Bearer <API_TOKEN>' -H 'Content-Type: application/json' -d '{"prompt": "A drone shot of a mountain range at sunrise", "resolution": "1080P"}' Evaluate a model output against structured Choice and Score questions using the jev structured evaluation model.
copy
$ curl https://api.cloudflare.com/client/v4/accounts/<ACCOUNT_ID>/ai/run/@cf/typesafe/jev -H 'Authorization: Bearer <API_TOKEN>' -H 'Content-Type: application/json' -d '{"state": "The response was accurate and concise.", "questions": [{"type": "Choice", "text": "Is the response helpful?"}, {"type": "Score", "text": "Rate response quality 1-5"}]}' Generate a high-quality image with gpt-image-2.5-sunburst using the xhigh quality setting for detailed output.
copy
$ curl https://api.cloudflare.com/client/v4/accounts/<ACCOUNT_ID>/ai/run/@cf/openai/gpt-image-2.5-sunburst -H 'Authorization: Bearer <API_TOKEN>' -H 'Content-Type: application/json' -d '{"prompt": "A photorealistic castle on a cliff at dusk", "quality": "xhigh"}'
Adds wan-3.0-prime (Alibaba text-to-video) supporting 480P, 720P, and 1080P output with adaptive aspect ratio and configurable duration.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds h3 multimodal video generation model supporting text-to-video, first/last frame image-to-video, and reference-to-video at 768P and 2K resolution. Adds h3-max fast multimodal video generation model supporting text-to-video and image-to-video at 480P and 768P. Adds gemini-omni-1.1-flash high-performance multimodal model for video generation and editing with conversational controls and generated audio. Adds gemini-omni-flash preview multimodal model for video generation and editing with conversational controls and generated audio.
+10 more
show less
Adds gemini-3.8-flash for long-horizon software engineering, autonomous agents, and complex enterprise workflows. Adds gpt-6-astra (OpenAI) for complex reasoning, coding, computer use, research, and document creation. Adds gpt-image-2.5-flare image generation model accepting text and image inputs with low, medium, high, xhigh, max, and auto quality settings. Adds gpt-image-2.5-sunburst image generation and editing model accepting text and image inputs with low, medium, high, xhigh, max, and auto quality settings. Adds gpt-oss-120b open-weight model for production, general-purpose, high-reasoning use cases. Adds gpt-oss-20b open-weight model optimized for lower latency, local, or specialized use cases. Adds union-alpha multimodal model for research, coding, and agentic workflows. Adds jev (TypeSafe) structured evaluation model supporting typed Noul, Choice, and Score questions with calibrated probabilities and confidence scores. Adds pareto (Unbiased) blended model that runs multiple language models in parallel per request and synthesizes a single API response, supporting text and vision inputs. Adds FLUX.2 [klein] 9B 9-billion-parameter image generation model with multi-reference editing capabilities.
15 details in Everything
Cloudflare adds Workflow instance deletion/streaming, Workers AI rejectIfBusy, RPC RPC Remote Procedure Call, a protocol that lets a program execute a function on another machine as if it were local, giving cyber tools a structured way to communicate across processes or hosts without managing raw sockets.
└──▷ TRY IT
Bulk-delete up to 100 Workflow instances by ID from a JSON file to free stored state and halt executions in one call.
copy
$ npx wrangler workflows instances delete my-workflow --filename ./instance-ids.json Fail a Workers AI inference call immediately when capacity is full, rather than waiting in a queue — useful in latency-sensitive request paths.
copy
$ curl --request POST \
--url "https://api.cloudflare.com/client/v4/accounts/$ACCOUNT_ID/ai/run/@cf/google/gemma-4-26b-a4b-it" \
--header "Authorization: Bearer $CLOUDFLARE_API_TOKEN" \
--header "Content-Type: application/json" \
--data '{"messages": [{"role": "user", "content": "Summarize this alert."}], "options": {"rejectIfBusy": true}}' Enable automatic RPC session span tracing across Workers and Durable Objects so the dashboard shows full call graphs without any code changes.
wrangler.toml
copy
[observability.traces]
enabled = true
Adds delete() and deleteBatch() methods on Workflow instance handles to remove one or up to 100 instances and free stored state, available via the Workflows API or wrangler workflows instances delete in Wrangler 4.125.0+; supports positional IDs, --filename with a JSON array file, the latest keyword, and --local for local dev sessions.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds WorkflowInstance.subscribe() method and GET /subscribe API endpoint to stream Workflow instance events (workflow, step, attempts, sleeps, waits, rollbacks) in real time, with filter and cursor options to scope the stream. Adds rejectIfBusy option as the third argument to the Workers AI binding and as options.rejectIfBusy: true in the native REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Workers traces now automatically capture JavaScript RPC session spans across Worker boundaries and Durable Objects — session spans, individual call spans, execution colors, and caller/callee arrows — enabled via observability.traces.enabled = true in the Wrangler configuration file; no SDK changes required. Enables Hyperdrive connectivity to PostgreSQL and MySQL databases from Python Workers.
+5 more
show less
Adds include, require, and exclude tag-based target criteria operators to Access for Infrastructure applications, with key-value tags manageable inline on targets or via the Resource Tagging API. R2 Data Catalog dashboard gains a Maintenance tab per table showing compaction and snapshot expiration schedules, a paginated audit log of recent runs with expandable operation metrics, and a Queue maintenance button for manual compaction requests. Session Recordings in Browser Run gain an Inspect panel with Console , Network , and DOMDOM The browser's in-memory tree representation of a web page's structure, standardized by the W3C, giving cyber tools a programmable interface to read or manipulate page content at runtime. HAR HAR An HTTP Archive file, a JSON-format log of all network requests and responses captured by a browser's developer tools, used by cyber tools to replay, inspect, or analyze web traffic without re-running a live session. Unified Routing is generally available for Cloudflare WAN and Magic Transit, enabling Automatic Return Routing, BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes. All Cloudflare customers can create additional Free accounts via the dashboard, via user-owned API tokens or OAuth access tokens access tokens A credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions.
Adds delete() and deleteBatch() methods on Workflow instance handles to remove one or up to 100 instances and free stored state, available via the Workflows API or wrangler workflows instances delete in Wrangler 4.125.0+; supports positional IDs, --filename with a JSON array file, the latest keyword, and --local for local dev sessions.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds WorkflowInstance.subscribe() method and GET /subscribe API endpoint to stream Workflow instance events (workflow, step, attempts, sleeps, waits, rollbacks) in real time, with filter and cursor options to scope the stream. Adds rejectIfBusy option as the third argument to the Workers AI binding and as options.rejectIfBusy: true in the native REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Enables Hyperdrive connectivity to PostgreSQL and MySQL databases from Python Workers. Adds include, require, and exclude tag-based target criteria operators to Access for Infrastructure applications, with key-value tags manageable inline on targets or via the Resource Tagging API.
+1 more
show less
Unified Routing is generally available for Cloudflare WAN and Magic Transit, enabling Automatic Return Routing, BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
4 more in Everything
Cloudflare API gains endpoints for Worker versions, deployments, secrets, assets, tails, and Workers for Platforms management︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Check which entitlements are active on an account to verify access controls before deploying a new Worker-based security policy.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/accounts/{account_id}/entitlements' \
-H 'Authorization: Bearer <API_TOKEN>'
Adds GET /accounts/{account_id}/entitlements and GET /zones/{zone_id}/entitlements endpoints to retrieve account- and zone-level entitlements.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Worker version lifecycle endpoints: List Worker Versions , Get Worker Version , Create Worker Version , Delete Worker Version , and Get Worker Script Version . Adds Worker deployment endpoints: List Worker Deployments , Create Worker Deployment , Get Worker Deployment , Delete Worker Deployment . Adds Worker secrets management endpoints: List secrets bound to a Worker script , Get a secret binding , Add a secret to a Worker script , Delete Worker script secret , and Patch multiple Worker script secrets . Adds Worker assets endpoints: Upload Worker Assets and Create Worker Assets Upload Session .
+17 more
show less
Adds Worker tail (live log streaming) endpoints: List Worker Tails , Start Worker Tail , Delete Worker Tail . Adds Worker script content and settings endpoints: Get Worker Script Content , Replace Worker Script Content , Get Worker Script Settings , Patch Worker Script Settings , Get Worker Script and Version Settings , Patch Worker Script and Version Settings . Adds Worker script subdomain endpoints: Get Worker Script Subdomain , Update Worker Script Subdomain , Delete Worker Script Subdomain . Adds Cron Trigger endpoints: Get Worker Script Schedules (Cron Triggers) and Update Worker Script Schedules (Cron Triggers). Adds Worker route endpoints: List Worker Routes , Get Worker Route , Create Worker Route , Replace Worker Route , Delete Worker Route . Adds Worker domain endpoints: List Worker Domains , Get Worker Domain , Attach Worker Domain , Detach Worker Domain . Adds Workers Subdomain endpoints: Get a Workers Subdomain , Create a Workers Subdomain , Delete Workers Subdomain . Adds Workers account settings endpoints: Fetch Workers Account Settings and Configure Workers Account Settings . Adds Worker script discovery endpoints: List Worker Scripts , Search Worker Scripts , Download Worker Script . Adds Durable Object endpoints: List Durable Object Namespaces and List Objects in a Durable Object namespace . Adds full Workers for Platforms Dispatch Namespace management: List , Get , Create , and Delete Workers for Platforms Dispatch Namespace . Adds Workers for Platforms script lifecycle endpoints: Get Workers for Platforms Script details , Upload Workers for Platforms Script Module , Delete Workers for Platforms Script , Get Workers for Platforms Script Content , Replace Workers for Platforms Script Content . Adds Workers for Platforms script secrets endpoints: List Workers for Platforms Script Secrets , Get Workers for Platforms Script Secret , Add a secret to a Workers for Platforms script , Delete Workers for Platforms script secret , Patch multiple Workers for Platforms script secrets . Adds Workers for Platforms script settings and bindings endpoints: Get Workers for Platforms Script Settings , Patch Workers for Platforms Script Settings , Get Workers for Platforms Script Bindings . Adds Workers for Platforms script tag management endpoints: List Workers for Platforms Script Tags , Replace Workers for Platforms Script Tags , Delete Workers for Platforms Script Tag . Adds Create Workers for Platforms Assets Upload Session endpoint for uploading static assets to a dispatch namespace script. Adds Create an Account endpoint to the API surface.
22 details in Everything
Cloudflare adds WAN unified routing GA, Hyperdrive Python support, Workflow batch deletes, and RPC RPC Remote Procedure Call, a protocol that lets a program execute a function on another machine as if it were local, giving cyber tools a structured way to communicate across processes or hosts without managing raw sockets.
Adds Inspect panel to Browser Run Session Recordings, exposing console output, network activity, and page structure for post-session debugging.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Unified Routing as generally available across supported WAN on-ramps in Cloudflare WAN. Enables deleting one or up to 100 Workflow instances and their stored state in a single operation via a binding or Wrangler. Adds a reject-busy mode for synchronous inference requests that fails immediately instead of waiting for capacity. Automatically includes JavaScript RPC session spans in Workers traces for Worker-to-Worker and Worker-to-Durable Object calls.
+1 more
show less
Adds Hyperdrive support for Python Workers, enabling connection pooling and query caching for PostgreSQL and MySQL.
Adds Inspect panel to Browser Run Session Recordings, exposing console output, network activity, and page structure for post-session debugging.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Unified Routing as generally available across supported WAN on-ramps in Cloudflare WAN. Enables deleting one or up to 100 Workflow instances and their stored state in a single operation via a binding or Wrangler. Adds a reject-busy mode for synchronous inference requests that fails immediately instead of waiting for capacity. Adds Hyperdrive support for Python Workers, enabling connection pooling and query caching for PostgreSQL and MySQL.
1 more in Everything
└──▷ BREAKING ON UPGRADE
! Starting in 2027, cloudflared will stop publishing releases for 32-bit Windows and Intel-based macOS architectures.
Browser Run adds session and DevTools methods to browser bindings
Sep 21, 2026
· release notes
Browser Run adds typed methods for session management, DevTools operations, and outbound routing via outboundByHost in browser bindings.
Adds the acquire() method to browser bindings for session acquisition Adds the launch() method to browser bindings with support for the outboundByHost configuration object Adds the connectSession(sessionId) method returning a session-pinned WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output. CDP CDP Cisco Discovery Protocol, a Cisco-proprietary Layer 2 protocol that advertises device identity, capabilities, and topology between directly connected Cisco gear, giving cyber tools a passive way to map network infrastructure. Adds typed session methods for Live View, active sessions, session history, limits, session details, and cleanup Adds nested devtools binding with typed methods for browser version, protocol descriptions, and target operations (list, create, activate, close)
5 details in Everything
Cloudflare One Client for macOS (version 2026.8.1755.1)
Sep 21, 2026
· release notes
Cloudflare One Client for macOS adds support for routing non-RFC 1918 RFC 1918 IETF standard that reserves three IPv4 address ranges (10.x, 172.16–31.x, 192.168.x) for private networks, never routed on the public internet, giving tools a reliable way to identify internal traffic.
Give teammates access to specific Workers directly from the dashboard
Sep 21, 2026
· release notes
Scoped Workers access: invite team members directly from the dashboard with granular role levels
Adds Invite button in the Workers dashboard to grant scoped access to specific Workers for teammates via email. Supports four new access levels for Worker invites: Metadata Read-Only, Content Read-Only, Editor, and Admin.
2 details in Everything
API surface changed: +61 endpoints, 112 modified, 10 deprecated︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
New endpoint DELETE /accounts/{account_id}/cloudforce-one/events/datasets/{dataset_id}/events︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New endpoint DELETE /accounts/{account_id}/cloudforce-one/events/event-categories/by-id/{category_id} New endpoint DELETE /accounts/{account_id}/cloudforce-one/events/tag-categories/{category_uuid} New endpoint DELETE /accounts/{account_id}/cloudforce-one/v2/credential-monitor/domains/{id} New endpoint DELETE /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/interests/{interest_id}
+71 more
show less
New endpoint DELETE /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/{priority_id} New endpoint DELETE /accounts/{account_id}/r2/buckets/{bucket_name}/lock New endpoint GET /accounts/{account_id}/cloudforce-one/events/by-id/{event_id}/relationships New endpoint GET /accounts/{account_id}/cloudforce-one/events/datasets/{dataset_id}/events/{event_id}/raw New endpoint GET /accounts/{account_id}/cloudforce-one/events/event-categories/by-id/{category_id} New endpoint GET /accounts/{account_id}/cloudforce-one/events/tag-categories/{category_uuid} New endpoint GET /accounts/{account_id}/cloudforce-one/events/tags/categories/actors New endpoint GET /accounts/{account_id}/cloudforce-one/v2/credential-monitor/domains New endpoint GET /accounts/{account_id}/cloudforce-one/v2/credential-monitor/matches New endpoint GET /accounts/{account_id}/cloudforce-one/v2/priority-intelligence New endpoint GET /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/constants New endpoint GET /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/interests New endpoint GET /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/interests/backtests/{backtest_id} New endpoint GET /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/interests/evaluations/{evaluation_id} New endpoint GET /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/{priority_id} New endpoint GET /accounts/{account_id}/cloudforce-one/v2/requests/legal-response/access-check New endpoint GET /accounts/{account_id}/cloudforce-one/v2/requests/{project_type} New endpoint GET /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/constants New endpoint GET /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/metadata New endpoint GET /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/quota New endpoint GET /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/types New endpoint GET /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/user/me New endpoint GET /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/{request_id} New endpoint GET /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/{request_id}/assets/list New endpoint GET /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/{request_id}/assets/{asset_id}/download New endpoint GET /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/{request_id}/messages New endpoint GET /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/{request_id}/messages/{message_id} New endpoint GET /accounts/{account_id}/security-center/insights/count New endpoint GET /accounts/{account_id}/workers/workers/{worker_id}/versions/latest New endpoint GET /analytics/sql New endpoint GET /analytics/sql/introspection New endpoint PATCH /accounts/{account_id}/cloudforce-one/events/event-categories/by-id/{category_id} New endpoint PATCH /accounts/{account_id}/cloudforce-one/events/tag-categories/{category_uuid} New endpoint PATCH /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/interests/{interest_id} New endpoint POST /accounts/{account_id}/browser-extension/config/logs/extension-events/search New endpoint POST /accounts/{account_id}/cloudforce-one/events New endpoint POST /accounts/{account_id}/cloudforce-one/events/event-categories/by-id/{category_id} New endpoint POST /accounts/{account_id}/cloudforce-one/v2/brand-protection/domain/matches/bulk-dismiss New endpoint POST /accounts/{account_id}/cloudforce-one/v2/brand-protection/domain/trial New endpoint POST /accounts/{account_id}/cloudforce-one/v2/brand-protection/queries/{query_id}/matches/{domain_id}/dismiss New endpoint POST /accounts/{account_id}/cloudforce-one/v2/brand-protection/queries/{query_id}/matches/{domain_id}/undismiss New endpoint POST /accounts/{account_id}/cloudforce-one/v2/credential-monitor/domains New endpoint POST /accounts/{account_id}/cloudforce-one/v2/priority-intelligence New endpoint POST /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/interests New endpoint POST /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/interests/backtests New endpoint POST /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/interests/evaluations New endpoint POST /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/quota New endpoint POST /accounts/{account_id}/cloudforce-one/v2/requests/{project_type} New endpoint POST /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/{request_id}/assets/upload New endpoint POST /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/{request_id}/messages/new New endpoint POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/skills/{skill_id}/diagnostic New endpoint POST /analytics/sql New endpoint PUT /accounts/{account_id}/cloudforce-one/v2/priority-intelligence/{priority_id} New endpoint PUT /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/{request_id} New endpoint PUT /accounts/{account_id}/cloudforce-one/v2/requests/{project_type}/{request_id}/messages/{message_id} New endpoint PUT /accounts/{account_id}/scim/v2/Groups/{group_id} GET /accounts/{account_id}/intel/attack-surface-report/issues: param source (query) added GET /accounts/{account_id}/intel/attack-surface-report/issues/class: param source (query) added GET /accounts/{account_id}/intel/attack-surface-report/issues/severity: param source (query) added GET /accounts/{account_id}/intel/attack-surface-report/issues/type: param source (query) added GET /accounts/{account_id}/realtime/kit/{app_id}/sessions/{session_id}/participants: param per_page (query) added GET /accounts/{account_id}/security-center/insights: param source (query) added GET /accounts/{account_id}/security-center/insights/class: param source (query) added GET /accounts/{account_id}/security-center/insights/severity: param source (query) added GET /accounts/{account_id}/security-center/insights/type: param source (query) added GET /zones/{zone_id}/security-center/insights: param source (query) added GET /zones/{zone_id}/security-center/insights/class: param source (query) added GET /zones/{zone_id}/security-center/insights/severity: param source (query) added GET /zones/{zone_id}/security-center/insights/type: param source (query) added POST /accounts: param Idempotency-Key (header) added POST /accounts/{account_id}/stream/live_inputs: param Idempotency-Key (header) added
76 details in Everything
└──▷ BREAKING ON UPGRADE
! DELETE /accounts/{account_id}/event_notifications/r2/{bucket_name}/configuration/queues/{queue_id}: param cf-r2-jurisdiction (header) removed! DELETE /accounts/{account_id}/r2/buckets/{bucket_name}: param cf-r2-jurisdiction (header) removed! DELETE /accounts/{account_id}/r2/buckets/{bucket_name}/cors: param cf-r2-jurisdiction (header) removed! DELETE /accounts/{account_id}/r2/buckets/{bucket_name}/domains/custom/{domain}: param cf-r2-jurisdiction (header) removed! DELETE /accounts/{account_id}/r2/buckets/{bucket_name}/objects: param cf-r2-jurisdiction (header) removed! DELETE /accounts/{account_id}/r2/buckets/{bucket_name}/objects/{object_key}: param cf-r2-jurisdiction (header) removed! DELETE /accounts/{account_id}/r2/buckets/{bucket_name}/sippy: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/event_notifications/r2/{bucket_name}/configuration: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/event_notifications/r2/{bucket_name}/configuration/queues/{queue_id}: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}/cors: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}/domains/custom: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}/domains/custom/{domain}: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}/domains/managed: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}/jobs: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}/jobs/{job_id}: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}/lifecycle: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}/lock: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}/objects: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}/objects/{object_key}: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}/sippy: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs: param cf-r2-jurisdiction (header) removed! GET /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs/{job_id}: param cf-r2-jurisdiction (header) removed! PATCH /accounts/{account_id}/r2/buckets/{bucket_name}: param cf-r2-jurisdiction (header) removed! POST /accounts/{account_id}/r2/buckets: param cf-r2-jurisdiction (header) removed! POST /accounts/{account_id}/r2/buckets/{bucket_name}/domains/custom: param cf-r2-jurisdiction (header) removed! POST /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs: param cf-r2-jurisdiction (header) removed! PUT /accounts/{account_id}/event_notifications/r2/{bucket_name}/configuration/queues/{queue_id}: param cf-r2-jurisdiction (header) removed! PUT /accounts/{account_id}/r2/buckets/{bucket_name}: param cf-r2-jurisdiction (header) removed! PUT /accounts/{account_id}/r2/buckets/{bucket_name}/cors: param cf-r2-jurisdiction (header) removed! PUT /accounts/{account_id}/r2/buckets/{bucket_name}/domains/custom/{domain}: param cf-r2-jurisdiction (header) removed! PUT /accounts/{account_id}/r2/buckets/{bucket_name}/domains/managed: param cf-r2-jurisdiction (header) removed! PUT /accounts/{account_id}/r2/buckets/{bucket_name}/lifecycle: param cf-r2-jurisdiction (header) removed! PUT /accounts/{account_id}/r2/buckets/{bucket_name}/lock: param cf-r2-jurisdiction (header) removed! PUT /accounts/{account_id}/r2/buckets/{bucket_name}/objects/{object_key}: param cf-r2-jurisdiction (header) removed! PUT /accounts/{account_id}/r2/buckets/{bucket_name}/sippy: param cf-r2-jurisdiction (header) removed! Deprecated endpoint DELETE /accounts/{account_id}/cloudforce-one/events/categories/{category_id} (still works)! Deprecated endpoint DELETE /accounts/{account_id}/cloudforce-one/events/tags/categories/{category_uuid} (still works)! Deprecated endpoint DELETE /accounts/{account_id}/cloudforce-one/events/{dataset_id}/delete (still works)! Deprecated endpoint GET /accounts/{account_id}/cloudforce-one/events/categories/{category_id} (still works)! Deprecated endpoint GET /accounts/{account_id}/cloudforce-one/events/raw/{dataset_id}/{event_id} (still works)! Deprecated endpoint GET /accounts/{account_id}/cloudforce-one/events/tags/categories/{category_uuid} (still works)! Deprecated endpoint GET /accounts/{account_id}/cloudforce-one/events/{event_id}/relationships (still works)! Deprecated endpoint PATCH /accounts/{account_id}/cloudforce-one/events/categories/{category_id} (still works)! Deprecated endpoint PATCH /accounts/{account_id}/cloudforce-one/events/tags/categories/{category_uuid} (still works)! Deprecated endpoint POST /accounts/{account_id}/cloudforce-one/events/categories/{category_id} (still works)
Inspect logs, network requests, and DOM in Session Recordings
Sep 18, 2026
· release notes
Browser Run Session Recordings now include an Inspect panel for logs, network requests, and DOM DOM The browser's in-memory tree representation of a web page's structure, standardized by the W3C, giving cyber tools a programmable interface to read or manipulate page content at runtime.
Adds the Inspect panel to Browser Run Session Recordings with Logs , Network , and DOM tabs Enables downloading session network activity as a HAR HAR An HTTP Archive file, a JSON-format log of all network requests and responses captured by a browser's developer tools, used by cyber tools to replay, inspect, or analyze web traffic without re-running a live session. Exposes recorded network activity via API as raw JSON or HAR file for external workflows Provides an expandable DOM view of the page structure at the end of the recording with HTML copy support
4 details in Everything
Filter DDoS attack traffic from Logpush jobs
Sep 18, 2026
· release notes
Logpush jobs can now exclude DDoS DDoS Distributed Denial of Service: an attack that floods a target system with traffic from many sources simultaneously, exhausting its resources so legitimate requests cannot be served.
Reject busy synchronous inference requests
Sep 17, 2026
· release notes
Adds rejectIfBusy option to Workers AI to fail synchronous inference requests immediately when capacity is unavailable
Adds rejectIfBusy config key for the options object in REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Adds third argument rejectIfBusy: true to the env.AI.run() binding signature
2 details in Everything
Create additional Free accounts through the dashboard and API
Sep 17, 2026
· release notes
Cloudflare adds self-service multi-account creation via dashboard, API and OAuth for Free plans
Adds self-serve flows in the Cloudflare dashboard allowing all customers to create additional Free accounts. Super Administrators can now create up to five Free accounts directly within an Enterprise Organization. Customers can programmatically create standalone Free accounts via User-owned API tokens or OAuth access tokens access tokens A credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions.
3 details in Everything
Workers traces now automatically include JavaScript RPC session spans
Sep 17, 2026
· release notes
Workers traces now automatically include JavaScript RPC RPC Remote Procedure Call, a protocol that lets a program execute a function on another machine as if it were local, giving cyber tools a structured way to communicate across processes or hosts without managing raw sockets.
observability.traces.enabled set to true in Wrangler config activates automatic tracing of JavaScript RPC session spansTraces now follow JavaScript RPC calls across Worker boundaries and into Durable Objects, showing caller-side session and method calls alongside callee invocation
2 details in Everything
Delete Workflow instances individually or in batches
Sep 17, 2026
· release notes
Wrangler 4.125.0 and Workflows API add support for deleting up to 100 workflow instances individually or in batches
└──▷ TRY IT
Target and remove the most recently created workflow instance from a Workers application.
copy
$ npx wrangler workflows instances delete my-workflow latest
Adds env.<WORKFLOW_BINDING>.delete() API method to delete a single Workflow instance by handle Adds env.<WORKFLOW_BINDING>.deleteBatch(["id1", "id2"]) API method to delete multiple Workflow instances in a single call Adds Wrangler 4.125.0 wrangler workflows instances delete <INSTANCE_ID> subcommand for CLI deletion Adds --filename flag to wrangler workflows instances delete to accept a JSON array of instance IDs Adds latest keyword as an argument to wrangler workflows instances delete to target the most recently created instance
+1 more
show less
Adds --local flag to wrangler workflows instances delete to operate against a local wrangler dev session
6 details in Everything
Cloudflare adds Workflow event streaming, Browser Run guardrails, DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
└──▷ TRY IT
Enforce BYOK BYOK Bring Your Own Key — a cloud deployment model where the customer supplies and controls the encryption keys rather than the provider, so sensitive data stays under the customer's cryptographic authority.
copy
$ curl -X PUT https://api.cloudflare.com/client/v4/accounts/<account_id>/ai-gateway/gateways/<gateway_id> \
-H 'Authorization: Bearer <token>' \
-H 'Content-Type: application/json' \
-d '{"byok_only": true}' Restrict a Browser Run session to a single domain so it cannot load external content — useful for screenshotting internal apps or sandboxed workflows.
copy
$ import puppeteer from '@cloudflare/puppeteer';
export async function startGuardedSession(env) {
const browser = await puppeteer.launch(env.MYBROWSER, {
guardrails: {
allowedDomains: ['example.com', '*.example.com'],
},
});
// browser cannot reach any hostname outside example.com
}
Adds WorkflowInstance.subscribe() method and GET /subscribe API endpoint to stream Workflow instance events (steps, attempts, sleeps, waits, rollbacks) without polling; supports filter for specific event types and cursor to start at a specific event.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds byok_only: true field on the PUT gateway API request to require provider credentials for AI Gateway third-party requests and prevent fallback to Unified Billing; adds per-request cf-aig-no-wholesale: true header for request-level enforcement. Adds include_shadow_metadata=true query parameter to the DNS records API to return shadow metadata identifying delegating NS records and glue A/AAAA records for shadowed DNS entries. Adds VoiceTurnMetrics typed summary to @cloudflare/voice v0.4.0 via addEventListener('turnmetrics', ...) , exposing per-turn turnId, terminal outcomes (completed, no_output, output_limit, content_filtered, model_error, tts_error, aborted), and stage timings (speech-to-final-transcript, model-to-first-text, TTS-to-first-audio, total turn duration). Adds per-Worker role-based access controls with four roles — Metadata Read-Only , Content Read-Only , Editor , and Admin — configurable via the Cloudflare dashboard, API, or Terraform for teammates, agents, and CI/CD workflows.
+3 more
show less
Extends Hyperdrive support to Python Workers for connecting to PostgreSQL and MySQL databases. Adds tagged targets and tag-based target criteria (include, require, exclude operators) to Access for Infrastructure, manageable inline or via the Resource Tagging API. Adds shadowed record warnings to all zones in the Cloudflare dashboard, identifying DNS records that will not be served due to subdomain delegation.
Adds WorkflowInstance.subscribe() method and GET /subscribe API endpoint to stream Workflow instance events (steps, attempts, sleeps, waits, rollbacks) without polling; supports filter for specific event types and cursor to start at a specific event.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds byok_only: true field on the PUT gateway API request to require provider credentials for AI Gateway third-party requests and prevent fallback to Unified Billing; adds per-request cf-aig-no-wholesale: true header for request-level enforcement. Adds include_shadow_metadata=true query parameter to the DNS records API to return shadow metadata identifying delegating NS records and glue A/AAAA records for shadowed DNS entries. Adds per-Worker role-based access controls with four roles — Metadata Read-Only , Content Read-Only , Editor , and Admin — configurable via the Cloudflare dashboard, API, or Terraform for teammates, agents, and CI/CD workflows. Extends Hyperdrive support to Python Workers for connecting to PostgreSQL and MySQL databases.
3 more in Everything
R2 Data Catalog adds table maintenance visibility and manual queueing
Sep 16, 2026
· release notes
R2 Data Catalog adds Maintenance tab with manual queueing, audit logs, and schema browser improvements.
Adds Maintenance tab to R2 Data Catalog table view for visibility into compaction and snapshot expiration settings, schedules, and next eligibility Adds Queue maintenance action in the R2 Data Catalog dashboard to manually request compaction jobs during normal scheduler polling Adds paginated audit log with job status, duration, and operation metrics for manifest rewrites, compaction, and snapshot expiration under Maintenance tab
3 details in Everything
Control JavaScript Detections API results
Sep 16, 2026
· release notes
Cloudflare Bot Management adds jsd_api_results_enabled config key to control whether JS Detections API results influence bot scoring.
Adds the jsd_api_results_enabled configuration key to allow Enterprise customers to toggle Cloudflare's consumption of JavaScript Detections API results for bot scoring.
1 detail in Everything
Hyperdrive support for Python Workers
Sep 16, 2026
· release notes
Adds Hyperdrive support for PostgreSQL and MySQL in Cloudflare Python Workers
Cloudflare AI adds Wan 3.0 Prime text-to-video, Gemini Flash variants, GPT Image 2.5 models, FLUX.2 klein, and OpenAI open-weight reasoning models.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds wan-3.0-prime, Alibaba's text-to-video model supporting adaptive aspect ratio and 480P, 720P, or 1080P resolution with configurable duration.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds gemini-3.8-flash, engineered for long-horizon software engineering, autonomous agents, and complex enterprise workflows. Adds gemini-omni-1.1-flash, a high-performance multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. Adds gemini-omni-flash, a preview high-performance multimodal video generation and editing model with conversational controls and generated audio. Adds gpt-image-2.5-flare, OpenAI's fast image generation model accepting text and image inputs with quality settings: low, medium, high, xhigh, max, and auto.
+4 more
show less
Adds gpt-image-2.5-sunburst, OpenAI's most capable image generation and editing model accepting text and image inputs with quality settings: low, medium, high, xhigh, max, and auto. Adds FLUX.2 [klein], a 9 billion parameter text-to-image model with multi-reference editing capabilities. Adds gpt-oss-120b, an OpenAI open-weight model for production, general-purpose, high-reasoning use cases. Adds gpt-oss-20b, an OpenAI open-weight model optimized for lower latency and local or specialized use cases.
9 details in Everything
Cloudflare adds SAML SAML A standard for passing signed identity assertions between a sign-in provider and an application. It lets a user sign in through their organization's identity provider.
└──▷ USE IT
Contain a browser automation workflow to a single domain so it cannot make requests to external hosts or exfiltrate data to third-party endpoints.
javascript
copy
puppeteer.launch(env.MYBROWSER, {
guardrails: {
allowedDomains: ["example.com", "*.example.com"]
}
});
Turn off Cloudflare-generated origin range requests for all traffic in a Cache Rule when your origin does not reliably honor Range headers.
json
copy
{
"expression": "true",
"action": "set_cache_settings",
"action_parameters": {
"origin_range_requests": {
"mode": "off"
}
}
}
Adds guardrails parameter to Browser Run sessions (Puppeteer, Playwright, REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. allowedDomains to restrict a browser session's HTTP/HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate. Adds { mode: "readonly" } option when generating a Browser Run Live View URL, letting observers watch a session without clicking, typing, navigating, or running JavaScript. Adds origin_range_requests.mode field (on, off, default) to Cache Rules in the Rulesets API, controlling whether Cloudflare fetches large files from origin in cache-aligned byte ranges. Adds force_authn API field (and Require reauthentication dashboard toggle) to Cloudflare Access SAML identity providers identity providers A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. ForceAuthn in SAML authentication requests to force fresh IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. false. Introduces new WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. command injection command injection An attack that makes an application execute operating-system commands supplied through untrusted input. It often happens when input is passed unsafely to a shell. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly.
+1 more
show less
Schedules additional WAF rules for 2026-09-22: SSRF jar HTTP loopback payload blocking, SSRF cloud/link-local non-standard IP notation, SSRF local non-standard IP notation, and SSTI SSTI Server-Side Template Injection, a vulnerability class where attacker-controlled input is evaluated by a server-side template engine, enabling remote code execution or data exfiltration.
Adds guardrails parameter to Browser Run sessions (Puppeteer, Playwright, REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. allowedDomains to restrict a browser session's HTTP/HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate. Adds { mode: "readonly" } option when generating a Browser Run Live View URL, letting observers watch a session without clicking, typing, navigating, or running JavaScript. Adds origin_range_requests.mode field (on, off, default) to Cache Rules in the Rulesets API, controlling whether Cloudflare fetches large files from origin in cache-aligned byte ranges.
3 more in Everything
Cloudflare adds fresh SAML SAML A standard for passing signed identity assertions between a sign-in provider and an application. It lets a user sign in through their organization's identity provider. WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Adds configuration to require fresh identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. Updates Cloudflare WAF managed rulesets with scheduled changes for 2026-09-22.
2 more in Everything
WAF - WAF Release - 2026-09-15 (2026-09-15)
Sep 15, 2026
· release notes
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. command injection command injection An attack that makes an application execute operating-system commands supplied through untrusted input. It often happens when input is passed unsafely to a shell.
Adds SSRF - Cloud detection (Rule ID: ...ca453d31) that blocks SSRF attempts targeting cloud metadata endpoints Adds Command Injection - Generic 10 detection (Rule ID: ...ba458b4b) that blocks generic command injection attempts Updates Version Control - Information Disclosure - Beta rule (ID: ...e540f17f), merged into the original rule and now blocking instead of logging
3 details in Everything
Access for Infrastructure now supports tagged targets and tag-based target criteria
Sep 15, 2026
· release notes
Access for Infrastructure now supports tagged targets and tag-based target criteria using include/require/exclude operators
Adds ability to attach key-value tags to infrastructure targets via central Resource Tagging API or inline management
1 detail in Everything
Stream Workflow instance events in your Worker or via the API with .subscribe()
Sep 15, 2026
· release notes
Stream Workflow instance events via API or .subscribe() without polling
Adds GET /subscribe API endpoint for streaming workflow and step events Adds WorkflowInstance.subscribe() method to Workers for subscribing to event history and live updates
2 details in Everything
Grant teammates and agents access to specific Workers
Sep 15, 2026
· release notes
Granular Worker permissions with Metadata Read-Only, Content Read-Only, Editor, Admin roles.
Adds four granular roles (Metadata Read-Only, Content Read-Only, Editor, Admin) for Workers to control access for teammates and agents. Enables configuration of Worker-level permissions via the Cloudflare dashboard, API, or Terraform. Durable Objects now inherit permissions from the implementing Worker.
3 details in Everything
Cloudflare: New endpoint DELETE /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{member_account_id}︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
New endpoint GET /accounts/{account_id}/browser-extension/config/inventories New endpoint GET /accounts/{account_id}/browser-extension/config/inventories/{registration_id} New endpoint GET /accounts/{account_id}/email-security/analytics/monthly_report New endpoint GET /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-runs New endpoint GET /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs
+4 more
show less
New endpoint GET /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs/{job_id} New endpoint POST /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs/{configuration_type}/queue New endpoint POST /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs New endpoint PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{member_account_id}
9 details in Everything
└──▷ BREAKING ON UPGRADE
! Removed endpoint DELETE /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{account_id}! Removed endpoint DELETE /accounts/{account_id}/workers/observability/metricsexport! Removed endpoint PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{account_id}! DELETE /accounts/{account_id}/pcaps/ownership/{ownership_id}: response schema changed! GET /accounts/{account_id}/pcaps: response schema changed! GET /accounts/{account_id}/pcaps/ownership: response schema changed! GET /accounts/{account_id}/pcaps/{pcap_id}: response schema changed! GET /accounts/{account_id}/pcaps/{pcap_id}/download: response schema changed! POST /accounts/{account_id}/pcaps: response schema changed! POST /accounts/{account_id}/pcaps/ownership: response schema changed! POST /accounts/{account_id}/pcaps/ownership/validate: response schema changed! POST /accounts/{account_id}/workers/observability/metricsexport: request body changed; response schema changed! PUT /accounts/{account_id}/pcaps/{pcap_id}/stop: response schema changed
Cloudflare: Adds per_cache_read_token and per_cache_write_token fields to the cf-aig-custom-cost header in AI Gateway, enabling custom cost metrics that reflect negotiated cache-read and cache-write token pricing across providers.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ USE IT
Track per-turn Voice Agent latency and failure reasons in real time to diagnose model errors, content filtering, or TTS failures.
text
copy
client.addEventListener('turnmetrics', (turn) => {
console.log(turn.outcome, turn.turnTotalMs);
});
Set different retention periods for successful and errored Workflow instances to control storage costs while keeping failure state for a full month.
text
copy
const instance = await env.MY_WORKFLOW.create({
retention: {
successRetention: '2 days',
errorRetention: '30 days'
},
});
Adds Cloudflare DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest. Adds support for routing non-RFC 1918 RFC 1918 IETF standard that reserves three IPv4 address ranges (10.x, 172.16–31.x, 192.168.x) for private networks, never routed on the public internet, giving tools a reliable way to identify internal traffic. MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies. Adds a service recovery mechanism backed by a Windows scheduler task to start the WARP service on system unlock in Cloudflare One Client for Windows (v2026.8.1290.1). Removes the requirement for the Windows WLAN AutoConfig service to be running in Cloudflare One Client for Windows (v2026.8.1290.1).
Adds Cloudflare DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest. Adds a service recovery mechanism backed by a Windows scheduler task to start the WARP service on system unlock in Cloudflare One Client for Windows (v2026.8.1290.1).
2 more in Everything
└──▷ BREAKING ON UPGRADE
! New Workflows created on or after September 10, 2026 on the Workers Paid plan default to a 7-day instance retention period (previously 30 days); existing Workflows are unaffected.
Cloudflare adds DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Adds Passive Detection for Data Loss Prevention — analyse Gateway traffic to discover where sensitive data travels before committing to a DLP policy.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New Workflows on Workers Paid retain instance state for seven days by default. Enables running Codex inside Cloudflare Containers via the OpenAI Agents API.
Adds Passive Detection for Data Loss Prevention — analyse Gateway traffic to discover where sensitive data travels before committing to a DLP policy.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enables running Codex inside Cloudflare Containers via the OpenAI Agents API.
1 more in Everything
└──▷ HOW TO FIND IT
Discover where sensitive data is flowing across Gateway traffic before writing a DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
📍 In the Cloudflare One dashboard, go to Gateway › Data Loss Prevention › Passive Detection, review sensitive data matches and their destinations, then use those findings to scope a new DLP policy.
Shadowed record warnings are now available for all zones
Sep 14, 2026
· release notes
Cloudflare adds shadowed record warnings for all zones and include_shadow_metadata API support
Adds UI warnings for shadowed DNS records in all zones to help identify delegated subdomains that Cloudflare does not authoritatively resolve Adds include_shadow_metadata=true parameter to the DNS records API to return delegation and glue record metadata
2 details in Everything
Require fresh authentication for SAML identity providers
Sep 14, 2026
· release notes
Cloudflare Access adds force_authn for SAML SAML A standard for passing signed identity assertions between a sign-in provider and an application. It lets a user sign in through their organization's identity provider.
Control which hostnames Browser Run sessions can access
Sep 14, 2026
· release notes
Browser Run now supports guardrails for hostname restriction and read-only Live View links
Adds guardrails.allowedDomains parameter to the Puppeteer launch function and REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate. Adds { mode: 'readonly' } option when generating a Live View URL to create read-only access links.
2 details in Everything
Prevent Unified Billing fallback for BYOK third-party providers
Sep 14, 2026
· release notes
AI Gateway adds byok_only setting and cf-aig-no-wholesale header to enforce BYOK BYOK Bring Your Own Key — a cloud deployment model where the customer supplies and controls the encryption keys rather than the provider, so sensitive data stays under the customer's cryptographic authority.
Adds byok_only boolean option in the gateway configuration (PUT request body) to prevent fallback to Unified Billing with Cloudflare-managed credentials
1 detail in Everything
Cloudflare: New endpoint DELETE /accounts/{account_id}/field_extractors/{extractor}
New endpoint GET /accounts/{account_id}/field_extractors/{extractor} New endpoint GET /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules New endpoint GET /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings New endpoint PATCH /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings New endpoint PUT /accounts/{account_id}/field_extractors/{extractor}
+6 more
show less
New endpoint PUT /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules GET /accounts/{account_id}/containers/applications/{application_id}/instances: param name_prefix (query) added; param state (query) added GET /accounts/{account_id}/gateway/lists: param direction (query) added; param filter (query) added; param order_by (query) added; param search (query) added GET /accounts/{account_id}/gateway/locations: param direction (query) added; param filter (query) added; param order_by (query) added; param search (query) added GET /accounts/{account_id}/gateway/proxy_endpoints: param direction (query) added; param filter (query) added; param order_by (query) added; param search (query) added GET /accounts/{account_id}/gateway/rules: param direction (query) added; param filter (query) added; param order_by (query) added; param search (query) added
11 details in Everything
└──▷ BREAKING ON UPGRADE
! Removed endpoint DELETE /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{account_id}! Removed endpoint DELETE /accounts/{account_id}/workers/observability/metricsexport! Removed endpoint PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{account_id}! DELETE /accounts/{account_id}/pcaps/ownership/{ownership_id}: response schema changed! GET /accounts/{account_id}/pcaps: response schema changed! GET /accounts/{account_id}/pcaps/ownership: response schema changed! GET /accounts/{account_id}/pcaps/{pcap_id}: response schema changed! GET /accounts/{account_id}/pcaps/{pcap_id}/download: response schema changed! POST /accounts/{account_id}/pcaps: response schema changed! POST /accounts/{account_id}/pcaps/ownership: response schema changed! POST /accounts/{account_id}/pcaps/ownership/validate: response schema changed! POST /accounts/{account_id}/workers/observability/metricsexport: request body changed; response schema changed! PUT /accounts/{account_id}/pcaps/{pcap_id}/stop: response schema changed
API surface changed: +20 endpoints, −3 endpoints, 162 modified︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
New endpoint DELETE /accounts/{account_id}/artifacts/namespaces/{namespace} New endpoint POST /accounts/{account_id}/artifacts/namespaces New endpoint POST /accounts/{account_id}/infrastructure/targets/batch_tags GET /accounts/{account_id}/infrastructure/targets: param tag (query) added GET /organizations/{organization_id}/accounts: param include_total (query) added
5 details in Everything
└──▷ BREAKING ON UPGRADE
! Removed endpoint DELETE /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{account_id}! Removed endpoint DELETE /accounts/{account_id}/workers/observability/metricsexport! Removed endpoint PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{account_id}! DELETE /accounts/{account_id}/pcaps/ownership/{ownership_id}: response schema changed! GET /accounts/{account_id}/pcaps: response schema changed! GET /accounts/{account_id}/pcaps/ownership: response schema changed! GET /accounts/{account_id}/pcaps/{pcap_id}: response schema changed! GET /accounts/{account_id}/pcaps/{pcap_id}/download: response schema changed! POST /accounts/{account_id}/pcaps: response schema changed! POST /accounts/{account_id}/pcaps/ownership: response schema changed! POST /accounts/{account_id}/pcaps/ownership/validate: response schema changed! POST /accounts/{account_id}/workers/observability/metricsexport: request body changed; response schema changed! PUT /accounts/{account_id}/pcaps/{pcap_id}/stop: response schema changed
Voice Agent turn metrics, AI Gateway cache token costs, Containers + OpenAI Agents API, and a new Zoom CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic.
└──▷ USE IT
Track where each Voice Agent turn spends time and how it ends — useful for diagnosing slow or failed turns in production.
text
copy
client.addEventListener('turnmetrics', (turn) => {
console.log(turn.outcome, turn.turnTotalMs);
});
Set per-instance retention so successful runs expire quickly while errored runs are kept for the full 30-day maximum — reducing storage costs without losing failure data.
text
copy
const instance = await env.MY_WORKFLOW.create({
retention: {
successRetention: '2 days',
errorRetention: '30 days'
},
});
Adds turnmetrics event on VoiceClient in @cloudflare/voice v0.4.0, emitting a typed VoiceTurnMetrics summary with turnId, terminal outcomes (completed, no_output, output_limit, content_filtered, model_error, tts_error, aborted), and per-stage timings (speech-to-final-transcript, model-to-first-text, TTS-to-first-audio, total turn duration).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds diagnostics: { browserConsole: true } option to withVoice() in @cloudflare/voice v0.4.0, forwarding server lifecycle events to the browser console for local debugging. Adds support for indexing R2 objects without filename extensions in AI Search when the objects include a supported Content-Type metadata value. Adds successRetention and errorRetention fields to WorkflowInstanceCreateOptions (via env.MY_WORKFLOW.create({ retention: { ... } }) ), letting you set per-instance retention periods for Cloudflare Workflows. Adds Cloudflare Containers as a self-hosted execution environment for the OpenAI Agents API (Codex), with a reference implementation via the open-source OpenAI Agents API Workers template.
+1 more
show less
Adds a new CASB integration for Zoom, connecting through Cloudflare's pre-built OAuth application with no manual app setup required.
Adds turnmetrics event on VoiceClient in @cloudflare/voice v0.4.0, emitting a typed VoiceTurnMetrics summary with turnId, terminal outcomes (completed, no_output, output_limit, content_filtered, model_error, tts_error, aborted), and per-stage timings (speech-to-final-transcript, model-to-first-text, TTS-to-first-audio, total turn duration).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds diagnostics: { browserConsole: true } option to withVoice() in @cloudflare/voice v0.4.0, forwarding server lifecycle events to the browser console for local debugging. Adds successRetention and errorRetention fields to WorkflowInstanceCreateOptions (via env.MY_WORKFLOW.create({ retention: { ... } }) ), letting you set per-instance retention periods for Cloudflare Workflows. Adds Cloudflare Containers as a self-hosted execution environment for the OpenAI Agents API (Codex), with a reference implementation via the open-source OpenAI Agents API Workers template. Adds a new CASB integration for Zoom, connecting through Cloudflare's pre-built OAuth application with no manual app setup required.
1 more in Everything
└──▷ BREAKING ON UPGRADE
! New Workflows created on or after September 10, 2026 on the Workers Paid plan now default to a seven-day retention period for completed and errored instances (previously 30 days). Existing Workflows are unaffected.
Cloudflare API v7.10.0 adds billing management, BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
└──▷ TRY IT
Enumerate BGP filter profiles for a Magic Transit account to audit which prefix filters are active.
copy
$ curl -s -X GET 'https://api.cloudflare.com/client/v4/accounts/{account_id}/magic/bgp/filter_profiles' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' List data-security posture policies to review all DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
copy
$ curl -s -X GET 'https://api.cloudflare.com/client/v4/accounts/{account_id}/data-security/posture/policies' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' Retrieve all submitted abuse reports for an account to integrate into a SOC SOC A security operations center, the team or function that monitors threats, investigates alerts and coordinates incident response. Its work can be internal, outsourced or shared.
copy
$ curl -s -X GET 'https://api.cloudflare.com/client/v4/accounts/{account_id}/abuse-reports/submitted' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json'
Adds POST /accounts/{account_id}/subscriptions/cancel-downgrade to cancel a delayed subscription downgrade.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds POST /accounts/{account_id}/subscriptions/{subscription_identifier}/cancel-reason and GET /accounts/{account_id}/subscriptions/{subscription_identifier}/cancel-reason to create and retrieve cancellation reasons. Adds POST /accounts/{account_id}/subscriptions/{subscription_identifier}/action/append to append a subscription action. Adds POST /accounts/{account_id}/bulk/subscriptions for bulk subscription creation. Adds full CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. GET/POST /accounts/{account_id}/payment-methods, GET/PUT/DELETE /accounts/{account_id}/payment-methods/{payment_method_id}, and POST /accounts/{account_id}/payment-methods/{payment_method_id}/set-as-default.
+15 more
show less
Adds GET /accounts/{account_id}/receipts/{receipt_id}/pdf to retrieve a receipt as a PDF. Adds POST /accounts/{account_id}/invoices to toggle PDF invoices. Adds POST /accounts/{account_id}/client-secret to create a Stripe setup intent for storing payment methods. Adds POST /accounts/{account_id}/billing/profile/payment-method to create a payment intent for a billing profile. Adds GET /accounts/{account_id}/billing/credits to retrieve account credits. Adds GET /accounts/{account_id}/billing/history to retrieve account billing history. Adds GET /accounts/{account_id}/billing/bad-debt to retrieve account bad-debt records. Adds GET /accounts/{account_id}/billing/unpaid-invoice to list unpaid invoices. Adds POST /billing/address-validation to validate a billing address. Adds GET /billing/rate_plans/{public_key} to look up a rate plan by public key. Adds GET /zones/{zone_id}/spectrum/protocols to list supported Spectrum application protocols. Adds full CRUD for data-security posture policies via GET/POST /accounts/{account_id}/data-security/posture/policies and GET/PUT/DELETE /accounts/{account_id}/data-security/posture/policies/{policy_id}. Adds GET/PUT/DELETE /accounts/{account_id}/field_extractors/{extractor} endpoints to manage field extractors. Adds GET /accounts/{account_id}/abuse-reports/submitted and GET /accounts/{account_id}/abuse-reports/submitted/{report_id} to list and retrieve submitted abuse reports. Adds GET /accounts/{account_id}/abuse-reports/submitted/{report_id}/emails to list emails sent to an abuse report submitter.
20 details in Everything
Cloudflare adds Voice Agent turn metrics, AI Gateway custom cache token costs, Container+Codex support, and R2 extensionless object indexing︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds per-turn latency metrics and browser diagnostics for Voice Agents via @cloudflare/voice v0.4.0.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Supports indexing extensionless R2 objects in AI Search by setting supported Content-Type metadata.
Adds per-turn latency metrics and browser diagnostics for Voice Agents via @cloudflare/voice v0.4.0.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
1 more in Everything
Cloudflare: Enables AI Search to index extensionless R2 objects by setting supported Content-Type metadata on those objects.
Cloudflare: New endpoint DELETE /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{member_account_id}︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
New endpoint GET /accounts/{account_id}/browser-extension/config/inventories New endpoint GET /accounts/{account_id}/browser-extension/config/inventories/{registration_id} New endpoint GET /accounts/{account_id}/email-security/analytics/monthly_report New endpoint GET /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-runs New endpoint GET /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs
+4 more
show less
New endpoint GET /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs/{job_id} New endpoint POST /accounts/{account_id}/r2-catalog/{bucket_name}/namespaces/{namespace}/tables/{table_name}/maintenance-configs/{configuration_type}/queue New endpoint POST /accounts/{account_id}/r2/buckets/{bucket_name}/storage-class-migration-jobs New endpoint PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{member_account_id}
9 details in Everything
└──▷ BREAKING ON UPGRADE
! Removed endpoint DELETE /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{account_id}! Removed endpoint DELETE /accounts/{account_id}/workers/observability/metricsexport! Removed endpoint PUT /accounts/{account_id}/addressing/address_maps/{address_map_id}/accounts/{account_id}! DELETE /accounts/{account_id}/pcaps/ownership/{ownership_id}: response schema changed! GET /accounts/{account_id}/pcaps: response schema changed! GET /accounts/{account_id}/pcaps/ownership: response schema changed! GET /accounts/{account_id}/pcaps/{pcap_id}: response schema changed! GET /accounts/{account_id}/pcaps/{pcap_id}/download: response schema changed! POST /accounts/{account_id}/pcaps: response schema changed! POST /accounts/{account_id}/pcaps/ownership: response schema changed! POST /accounts/{account_id}/pcaps/ownership/validate: response schema changed! POST /accounts/{account_id}/workers/observability/metricsexport: request body changed; response schema changed! PUT /accounts/{account_id}/pcaps/{pcap_id}/stop: response schema changed
Cloudflare adds Zoom CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic.
└──▷ USE IT
Keep completed Workflow instances for 2 days but retain errored instances for the full 30 days to balance storage costs with debuggability on Workers Paid.
javascript
copy
const instance = await env.MY_WORKFLOW.create({
retention: {
successRetention: "2 days",
errorRetention: "30 days"
},
});
Pass negotiated cache pricing to AI Gateway so custom cost dashboards accurately reflect provider cache-read and cache-write rates alongside standard token costs.
copy
$ curl https://gateway.ai.cloudflare.com/v1/<account_id>/<gateway_id>/openai/chat/completions \
-H 'Content-Type: application/json' \
-H 'cf-aig-custom-cost: {"per_token_in": "0.000003", "per_token_out": "0.000015", "per_cache_read_token": "0.0000003", "per_cache_write_token": "0.0000015"}' \
-d '{"model": "gpt-4o", "messages": [{"role": "user", "content": "Hello"}]}' Enable the new Zoom CASB integration to continuously scan your organisation's Zoom account for meeting security misconfigurations and DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
📍 In the Cloudflare One dashboard, go to Cloud & SaaS findings › Integrations, select Zoom, and authenticate via the pre-built OAuth application. Scanning begins immediately and surfaces findings within minutes.
Adds successRetention and errorRetention fields to WorkflowInstanceCreateOptions to set per-instance or per-Workflow retention periods (e.g., '2 days', '30 days') on Workers Paid; maximum remains 30 days.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Cloudflare Containers now supports self-hosted execution environments for the OpenAI Agents API via Codex, with a reference implementation available as the open-source OpenAI Agents API Workers template. Adds a new Cloudflare CASB integration for Zoom, scanning account settings, user accounts, meetings, recordings, and content (via DLP Profile matching) for security findings; enable under Cloud & SaaS findings > Integrations in the Cloudflare One dashboard. Adds support for routing non-RFC 1918 RFC 1918 IETF standard that reserves three IPv4 address ranges (10.x, 172.16–31.x, 192.168.x) for private networks, never routed on the public internet, giving tools a reliable way to identify internal traffic. MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies. Adds support for routing non-RFC 1918 local IPv4 networks through the WARP tunnel in Cloudflare One Client for Windows (2026.8.1290.1) when unrestricted LAN inclusion is enabled by policy or MDM.
+3 more
show less
Cloudflare One Client for Windows (2026.8.1290.1) no longer requires the Windows WLAN AutoConfig service to be running. Cloudflare One Client for Windows (2026.8.1290.1) adds a service recovery mechanism backed by a Windows scheduler task to restart the WARP service on system unlock if not already running. Browser Isolation on iOS now displays the tap-to-type prompt inline over the focused text field instead of as a full-screen overlay, reducing disruption during text entry in isolated sessions.
Adds successRetention and errorRetention fields to WorkflowInstanceCreateOptions to set per-instance or per-Workflow retention periods (e.g., '2 days', '30 days') on Workers Paid; maximum remains 30 days.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Cloudflare Containers now supports self-hosted execution environments for the OpenAI Agents API via Codex, with a reference implementation available as the open-source OpenAI Agents API Workers template. Adds a new Cloudflare CASB integration for Zoom, scanning account settings, user accounts, meetings, recordings, and content (via DLP Profile matching) for security findings; enable under Cloud & SaaS findings > Integrations in the Cloudflare One dashboard.
5 more in Everything
└──▷ BREAKING ON UPGRADE
! New Workflows created on or after September 10, 2026 on the Workers Paid plan default to a seven-day retention period (previously 30 days); existing Workflows are unaffected, but teams relying on the 30-day default for new Workflows must now explicitly set successRetention or errorRetention to preserve that duration.
Cloudflare: Adds POST /accounts/{account_id}/payment-methods/{payment_method_id}/set-as-default to designate a default payment method.
└──▷ TRY IT
Retrieve all unpaid invoices for an account to automate dunning or alerting workflows.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/accounts/{account_id}/billing/unpaid-invoice' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' List BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/accounts/{account_id}/magic/bgp/filter_profiles' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' Retrieve a Content Scanning field extractor definition to inspect custom extraction rules for a zone.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/accounts/{account_id}/field_extractors/{extractor}' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json'
Adds GET /user/spectrum_analytics/zones/report for Spectrum Analytics zone bandwidth reports. Adds Workers build pipeline endpoints: start, list, cancel, get builds; stream logs; manage triggers, variables, deploy hooks, tokens, repo connections.
2 details in Everything
Cloudflare: Adds cache-read and cache-write custom token rate configuration for requests routed through AI Gateway, enabling cost tracking for cached responses.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds a new CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic. Supports running Codex with Cloudflare Containers via the OpenAI Agents API. Sets default instance retention for new Workflows on Workers Paid to seven days.
Adds a new CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic. Supports running Codex with Cloudflare Containers via the OpenAI Agents API.
1 more in Everything
Cloudflare: Sets default Workflow instance retention on Workers Paid to seven days for new Workflows.
AI Search supports extensionless R2 objects with Content-Type metadata
Sep 11, 2026
· release notes
AI Search now indexes extensionless R2 objects if they include supported Content-Type metadata.
Inspect Voice Agent turn latency and outcomes
Sep 11, 2026
· release notes
@cloudflare/voice v0.4.0 adds turn-level diagnostics and browserConsole config for Voice Agent agents
@cloudflare/voice v0.4.0 emits typed VoiceTurnMetrics summaries via the turnmetrics event, exposing terminal outcomes (completed, no_output, output_limit, content_filtered, model_error, tts_error, or aborted) and stage timings.
1 detail in Everything
API surface changed: +7 endpoints, −1 endpoint, 58 modified︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
API change API surface changed: +7 endpoints, −1 endpoint, 58 modified︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
+ DELETE /accounts/{account_id}/field_extractors/{extractor} + GET /accounts/{account_id}/field_extractors/{extractor} + GET /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules + GET /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings + PATCH /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings + PUT /accounts/{account_id}/field_extractors/{extractor} + PUT /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules
~ DELETE /accounts/{account_id}/custom_ns/{custom_ns_id}: request body changed ~ DELETE /accounts/{account_id}/devices/deployment-groups/{group_id}: response schema changed ~ DELETE /accounts/{account_id}/devices/ip-profiles/{profile_id}: response schema changed ~ DELETE /accounts/{account_id}/devices/physical-devices/{device_id}: response schema changed ~ DELETE /accounts/{account_id}/devices/registrations: response schema changed ~ DELETE /accounts/{account_id}/devices/registrations/{registration_id}: response schema changed ~ DELETE /accounts/{account_id}/secondary_dns/acls/{acl_id}: request body changed ~ DELETE /accounts/{account_id}/secondary_dns/peers/{peer_id}: request body changed ~ DELETE /accounts/{account_id}/secondary_dns/tsigs/{tsig_id}: request body changed ~ DELETE /accounts/{account_id}/workers/observability/destinations/{slug}: response schema changed ~ DELETE /zones/{zone_id}/secondary_dns/incoming: request body changed ~ DELETE /zones/{zone_id}/secondary_dns/outgoing: request body changed ~ GET /accounts/{account_id}/containers/applications/{application_id}/instances: param name_prefix (query) added; param state (query) added ~ GET /accounts/{account_id}/devices/client-versions: response schema changed ~ GET /accounts/{account_id}/devices/client-versions/target-environments: response schema changed ~ GET /accounts/{account_id}/devices/deployment-groups: response schema changed ~ GET /accounts/{account_id}/devices/deployment-groups/{group_id}: response schema changed ~ GET /accounts/{account_id}/devices/ip-profiles: response schema changed ~ GET /accounts/{account_id}/devices/ip-profiles/{profile_id}: response schema changed ~ GET /accounts/{account_id}/devices/physical-devices: response schema changed ~ GET /accounts/{account_id}/devices/physical-devices/{device_id}: response schema changed ~ GET /accounts/{account_id}/devices/registrations: response schema changed ~ GET /accounts/{account_id}/devices/registrations/{registration_id}: response schema changed ~ GET /accounts/{account_id}/devices/registrations/{registration_id}/override_codes: response schema changed ~ GET /accounts/{account_id}/flagship/apps/{app_id}/flags: response schema changed ~ GET /accounts/{account_id}/flagship/apps/{app_id}/flags/{flag_key}: response schema changed ~ GET /accounts/{account_id}/gateway/lists: param direction (query) added; param filter (query) added; param order_by (query) added; param search (query) added ~ GET /accounts/{account_id}/gateway/locations: param direction (query) added; param filter (query) added; param order_by (query) added; param search (query) added ~ GET /accounts/{account_id}/gateway/proxy_endpoints: param direction (query) added; param filter (query) added; param order_by (query) added; param search (query) added ~ GET /accounts/{account_id}/gateway/rules: param direction (query) added; param filter (query) added; param order_by (query) added; param search (query) added ~ GET /accounts/{account_id}/images/v2: response schema changed ~ GET /accounts/{account_id}/moq/relays: response schema changed ~ GET /accounts/{account_id}/workers/observability/metricsexport: response schema changed ~ PATCH /accounts/{account_id}/devices/deployment-groups/{group_id}: response schema changed ~ PATCH /accounts/{account_id}/devices/ip-profiles/{profile_id}: response schema changed ~ PATCH /accounts/{account_id}/devices/policy: request body changed ~ PATCH /accounts/{account_id}/devices/policy/{policy_id}: request body changed ~ POST /accounts/{account_id}/abuse-reports/{report_id}/mitigations/appeal: response schema changed ~ POST /accounts/{account_id}/calls/apps: response schema changed ~ POST /accounts/{account_id}/calls/turn_keys: response schema changed ~ POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/feeds/poll: response schema changed ~ POST /accounts/{account_id}/devices/deployment-groups: response schema changed ~ POST /accounts/{account_id}/devices/ip-profiles: response schema changed ~ POST /accounts/{account_id}/devices/physical-devices/{device_id}/revoke: response schema changed ~ POST /accounts/{account_id}/devices/policy: request body changed ~ POST /accounts/{account_id}/devices/registrations/revoke: response schema changed ~ POST /accounts/{account_id}/devices/registrations/unrevoke: response schema changed ~ POST /accounts/{account_id}/flagship/apps/{app_id}/flags: response schema changed ~ POST /accounts/{account_id}/logpush/jobs: request body changed ~ POST /accounts/{account_id}/workers/observability/metricsexport: request body changed; response schema changed ~ POST /zones/{zone_id}/logpush/jobs: request body changed ~ POST /zones/{zone_id}/secondary_dns/force_axfr: request body changed ~ POST /zones/{zone_id}/secondary_dns/outgoing/disable: request body changed ~ POST /zones/{zone_id}/secondary_dns/outgoing/enable: request body changed ~ POST /zones/{zone_id}/secondary_dns/outgoing/force_notify: request body changed ~ PUT /accounts/{account_id}/flagship/apps/{app_id}/flags/{flag_key}: response schema changed ~ PUT /accounts/{account_id}/logpush/jobs/{job_id}: request body changed ~ PUT /zones/{zone_id}/logpush/jobs/{job_id}: request body changed
− DELETE /accounts/{account_id}/workers/observability/metricsexport (breaking)
New endpoint DELETE /accounts/{account_id}/field_extractors/{extractor}︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New endpoint GET /accounts/{account_id}/field_extractors/{extractor} New endpoint GET /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules New endpoint GET /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings New endpoint PATCH /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/settings
+7 more
show less
New endpoint PUT /accounts/{account_id}/field_extractors/{extractor} New endpoint PUT /accounts/{account_id}/workers/observability/zones/{zone_id}/observability/tracing/rules GET /accounts/{account_id}/containers/applications/{application_id}/instances: param name_prefix (query) added; param state (query) added GET /accounts/{account_id}/gateway/lists: param direction (query) added; param filter (query) added; param order_by (query) added; param search (query) added GET /accounts/{account_id}/gateway/locations: param direction (query) added; param filter (query) added; param order_by (query) added; param search (query) added GET /accounts/{account_id}/gateway/proxy_endpoints: param direction (query) added; param filter (query) added; param order_by (query) added; param search (query) added GET /accounts/{account_id}/gateway/rules: param direction (query) added; param filter (query) added; param order_by (query) added; param search (query) added
12 details in Everything
└──▷ BREAKING ON UPGRADE
! Removed endpoint DELETE /accounts/{account_id}/workers/observability/metricsexport! POST /accounts/{account_id}/workers/observability/metricsexport: request body changed; response schema changed
Cloudflare: Adds successRetention and errorRetention fields to WorkflowInstanceCreateOptions (via env.MY_WORKFLOW.create({ retention: { ... } }) ) to control per-instance state retention on Workers Workflows, with a new seven-day default for Workers Paid (previously 30 days); maximum remains 30 days.
└──▷ USE IT
Set per-instance retention on a Workflow so successful runs are pruned after 2 days but errored runs are kept for the maximum 30 days, reducing storage costs while preserving failure state for debugging.
javascript
copy
const instance = await env.MY_WORKFLOW.create({
retention: {
successRetention: "2 days",
errorRetention: "30 days"
},
});
Check your Worker bundle size against the new 64 MiB uncompressed limit before deploying to catch oversized bundles in CI without actually uploading.
copy
$ wrangler deploy --outdir bundled/ --dry-run
R2 Data Access Logs are now generally available, recording object read, write, list, multipart upload, and delete operations (with response status codes) across the S3-compatible S3-compatible An object-storage API that mirrors Amazon S3's HTTP interface, so any client or cyber tool written for AWS S3 works unchanged against any compliant storage backend. r2.dev or custom domains; events appear in Workers Observability and are filterable by bucket, operation, interface, and actor. Raises the Workers bundle size limit to 64 MiB (uncompressed) across both Free and Paid plans, removing the previous compressed-size limits of 3 MB (Free) and 10 MB (Paid); use wrangler deploy --outdir bundled/ --dry-run to check bundle size before deploying. Cloudflare One Appliance dashboard now supports defining custom applications — matched by hostnames, IP subnets, and the new Source subnets field — for breakout and prioritized traffic steering, without requiring API calls. Cloudflare One Appliance dashboard now supports configuring custom DHCP options (including PXE/iPXE boot, VoIP provisioning, and vendor-specific config) directly from the LAN configuration panel. Cloudflare One Client for macOS (2026.8.1290.1 beta) adds support for routing non-RFC 1918 RFC 1918 IETF standard that reserves three IPv4 address ranges (10.x, 172.16–31.x, 192.168.x) for private networks, never routed on the public internet, giving tools a reliable way to identify internal traffic. MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies.
+2 more
show less
Cloudflare One Client for Windows (2026.8.1290.1 beta) adds support for routing non-RFC 1918 local IPv4 networks through the WARP tunnel when unrestricted LAN inclusion is enabled by policy or MDM, removes the requirement for the Windows WLAN AutoConfig service, and adds a service recovery mechanism via Windows scheduler task to restart the WARP service on system unlock. WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF - Cloud - 3 and Command Injection - Generic 10.
R2 Data Access Logs are now generally available, recording object read, write, list, multipart upload, and delete operations (with response status codes) across the S3-compatible S3-compatible An object-storage API that mirrors Amazon S3's HTTP interface, so any client or cyber tool written for AWS S3 works unchanged against any compliant storage backend. r2.dev or custom domains; events appear in Workers Observability and are filterable by bucket, operation, interface, and actor. WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF - Cloud - 3 and Command Injection - Generic 10.
5 more in Everything
└──▷ BREAKING ON UPGRADE
! Miniflare v5 removes deprecated APIs and options including legacy alpha D1 bindings, internal APIs like wrappedBindings, and built-in module discovery; moves local-only /cdn-cgi routes under /cdn-cgi/local; replaces per-resource persistence options with shared persistence root options.! Workers Workflows created on or after September 10, 2026 on the Workers Paid plan default to a seven-day instance retention period (down from 30 days); existing Workflows are unaffected.
Cloudflare: New Workflows on Workers Paid retain instance state for seven days by default.
Improves iOS tap-to-type experience in Browser Isolation by displaying an inline prompt.
1 more in Everything
Cloudflare: Adds per_cache_read_token and per_cache_write_token fields to the cf-aig-custom-cost header in AI Gateway custom costs, enabling cache-read and cache-write token rates to reflect negotiated cache pricing; an omitted cache rate defaults to per_token_in.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Check your Worker's uncompressed bundle size before deploying to ensure it stays under the new 64 MiB limit.
copy
$ wrangler deploy --outdir bundled/ --dry-run Pass cache-token pricing to AI Gateway so custom cost metrics reflect negotiated cache rates from your provider.
copy
$ curl https://gateway.ai.cloudflare.com/v1/<account_id>/<gateway_id>/openai/chat/completions \
-H 'cf-aig-custom-cost: {"per_token_in": "0.000003", "per_token_out": "0.000015", "per_cache_read_token": "0.0000005", "per_cache_write_token": "0.0000015"}' \
-H 'Content-Type: application/json' \
-d '{"model": "gpt-4o", "messages": [{"role": "user", "content": "Hello"}]}' Deploy a Django app to Python Workers using the new WSGI WSGI A Python standard (PEP 3333) defining how a web server passes HTTP requests to a Python application, letting frameworks and servers interoperate without custom glue code.
python
copy
# worker.py
from workers import wsgi
from django.core.wsgi import get_wsgi_application
app = get_wsgi_application()
Default = wsgi.entrypoint(app)
Supports wsgi and asgi modules from the workers package in Python Workers, enabling WSGI frameworks (Django, Flask) via wsgi.entrypoint(app) and ASGI ASGI A Python async web server interface specification that defines how servers and applications exchange HTTP and WebSocket messages; cyber tools use it to serve high-concurrency APIs without blocking on I/O. asgi.entrypoint(app) . Adds R2 Data Access Logs (GA) for non-jurisdictional buckets, recording object read, write, list, multipart upload, and delete operations with response status codes; filterable in Workers Observability by bucket, operation, interface, actor, and other request fields. Raises the Workers bundle size limit to 64 MiB (uncompressed) across all plans, removing the previous 3 MB (Free) and 10 MB (Paid) compressed-size checks; use wrangler deploy --outdir bundled/ --dry-run to inspect bundle size before deploying. Adds Load Balancing pool sets via the API, combining geographic matching (Cloudflare data center, country, or region) with location-specific steering policies, pool weights, and fallback pools in a single load balancer. Adds Source subnets field for custom application definitions in Cloudflare One Appliance Traffic Steering (Breakout and Prioritized traffic), allowing traffic matching by source IP range directly from the dashboard.
+1 more
show less
Enables configuration of custom DHCP options directly from the Cloudflare One Appliance dashboard under LAN configuration > DHCP server options , including PXE/iPXE boot, VoIP provisioning, and arbitrary option codes.
Supports wsgi and asgi modules from the workers package in Python Workers, enabling WSGI frameworks (Django, Flask) via wsgi.entrypoint(app) and ASGI ASGI A Python async web server interface specification that defines how servers and applications exchange HTTP and WebSocket messages; cyber tools use it to serve high-concurrency APIs without blocking on I/O. asgi.entrypoint(app) . Adds R2 Data Access Logs (GA) for non-jurisdictional buckets, recording object read, write, list, multipart upload, and delete operations with response status codes; filterable in Workers Observability by bucket, operation, interface, actor, and other request fields. Adds Load Balancing pool sets via the API, combining geographic matching (Cloudflare data center, country, or region) with location-specific steering policies, pool weights, and fallback pools in a single load balancer.
3 more in Everything
└──▷ BREAKING ON UPGRADE
! Miniflare v5 removes deprecated APIs and options including legacy alpha D1 bindings.! Miniflare v5 removes internal APIs such as wrappedBindings.! Miniflare v5 removes built-in module discovery; the module graph must now be provided by higher-level tools like Wrangler or the Vite plugin.! Miniflare v5 moves local-only /cdn-cgi routes under /cdn-cgi/local.! Miniflare v5 replaces per-resource persistence options with shared persistence root options.
Cloudflare adds R2 Data Access Logs GA, 64 MiB Worker size limit, Images text rasterization, WSGI WSGI A Python standard (PEP 3333) defining how a web server passes HTTP requests to a Python application, letting frameworks and servers interoperate without custom glue code. ASGI ASGI A Python async web server interface specification that defines how servers and applications exchange HTTP and WebSocket messages; cyber tools use it to serve high-concurrency APIs without blocking on I/O.
└──▷ TRY IT
Check your Worker's uncompressed bundle size before deploying to confirm it falls within the new 64 MiB limit.
copy
$ wrangler deploy --outdir bundled/ --dry-run Pass negotiated cache-token pricing to AI Gateway so custom cost metrics account for cache-read and cache-write rates separately from standard input tokens.
json
copy
{
"per_token_in": "0.000001",
"per_token_out": "0.000003",
"per_cache_read_token": "0.0000005",
"per_cache_write_token": "0.000001"
}
Use WSGI to run a Django app inside a Python Worker, routing all incoming requests through the Django application stack.
python
copy
from workers import wsgi
from django.core.wsgi import get_wsgi_application
app = get_wsgi_application()
Default = wsgi.entrypoint(app)
Adds per_cache_read_token and per_cache_write_token fields to the cf-aig-custom-cost header in AI Gateway, enabling custom cost metrics to reflect negotiated cache pricing for cache-read and cache-write token rates.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds filter.metadata parameter to the .list() method in the Images binding, enabling metadata-based filtering with range operators such as { gte: 2, lte: 5 }. Adds wsgi.fetch() method from the workers module for manual control of WSGI dispatch inside a WorkerEntrypoint class. R2 Data Access Logs are now generally available, recording object read, write, list, multipart upload, and delete operations with response status codes; events are accessible in Workers Observability and filterable by bucket, operation, interface, actor, and other request fields. Raises the Worker bundle size limit to 64 MiB (uncompressed) across all plans — free and paid — removing the previous compressed-size caps of 3 MB (Free) and 10 MB (Paid); wrangler deploy --outdir bundled/ --dry-run reports the Total Upload uncompressed size.
+2 more
show less
Adds Source subnets field to the Cloudflare One Appliance dashboard for matching breakout and prioritized traffic by source IP range, alongside Hostnames and IP subnets, without requiring API calls. Adds Add DHCP option and Add custom option controls to LAN configuration in the Cloudflare One Appliance dashboard for configuring DHCP options (PXE/iPXE boot, VoIP, vendor-specific) without requiring API calls.
Adds per_cache_read_token and per_cache_write_token fields to the cf-aig-custom-cost header in AI Gateway, enabling custom cost metrics to reflect negotiated cache pricing for cache-read and cache-write token rates.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds wsgi.fetch() method from the workers module for manual control of WSGI dispatch inside a WorkerEntrypoint class. R2 Data Access Logs are now generally available, recording object read, write, list, multipart upload, and delete operations with response status codes; events are accessible in Workers Observability and filterable by bucket, operation, interface, actor, and other request fields. Adds Add DHCP option and Add custom option controls to LAN configuration in the Cloudflare One Appliance dashboard for configuring DHCP options (PXE/iPXE boot, VoIP, vendor-specific) without requiring API calls.
3 more in Everything
└──▷ BREAKING ON UPGRADE
! Miniflare v5 removes deprecated APIs and options including legacy alpha D1 bindings.! Miniflare v5 removes internal APIs such as wrappedBindings.! Miniflare v5 removes built-in module discovery; the module graph must now be provided by higher-level tools such as Wrangler or the Vite plugin.! Miniflare v5 moves local-only /cdn-cgi routes under /cdn-cgi/local.! Miniflare v5 replaces per-resource persistence options with shared persistence root options.
Cloudflare: Adds full CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. GET/POST /accounts/{account_id}/payment-methods, GET/PUT/DELETE /accounts/{account_id}/payment-methods/{payment_method_id}, and POST /accounts/{account_id}/payment-methods/{payment_method_id}/set-as-default.
└──▷ TRY IT
List all BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
copy
$ curl -s -X GET 'https://api.cloudflare.com/client/v4/accounts/{account_id}/magic/bgp/filter_profiles' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' Retrieve all supported Spectrum application protocols for a zone to validate what L4 protocols are available.
copy
$ curl -s -X GET 'https://api.cloudflare.com/client/v4/zones/{zone_id}/spectrum/protocols' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' Retrieve unpaid invoices for an account to integrate into an automated billing reconciliation workflow.
copy
$ curl -s -X GET 'https://api.cloudflare.com/client/v4/accounts/{account_id}/billing/unpaid-invoice' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json'
Adds POST /accounts/{account_id}/pay-invoice and POST /accounts/{account_id}/pay-bad-debt to pay invoices and bad debt directly via API. Adds GET /accounts/{account_id}/billing/credits, GET /accounts/{account_id}/billing/history, GET /accounts/{account_id}/billing/bad-debt, and GET /accounts/{account_id}/billing/unpaid-invoice for account billing visibility. Adds full CRUD for BGP filter profiles via GET/POST /accounts/{account_id}/magic/bgp/filter_profiles and GET/PUT/DELETE /accounts/{account_id}/magic/bgp/filter_profiles/{profile_id}. Adds full CRUD for field extractors via GET/PUT/DELETE /accounts/{account_id}/field_extractors/{extractor}.
4 details in Everything
AI Gateway gains custom cache token pricing, Radar search covers Internet events, and Python Workers now support Python 3.14︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Supports setting custom cache-read and cache-write token rates for requests routed through AI Gateway.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ R2 Data Access Logs now record object operations with response status codes below 400 and expose per-request events in Workers Observability. Browser Isolation displays an inline tap-to-type prompt for iOS users.
Supports setting custom cache-read and cache-write token rates for requests routed through AI Gateway.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ R2 Data Access Logs now record object operations with response status codes below 400 and expose per-request events in Workers Observability.
1 more in Everything
Cloudflare: Python Workers now support Python 3.14.
Default instance retention for new Workflows on Workers Paid is seven days
Sep 10, 2026
· release notes
Cloudflare Workers Workflows Paid plan default instance retention reduced to seven days; successRetention/errorRetention API fields now actionable.
Reduces the default retention period for completed and errored Workflow instances created on the Workers Paid plan to seven days (from 30 days) effective September 10, 2026.
1 detail in Everything
└──▷ BREAKING ON UPGRADE
! New Workflows on the Workers Paid plan created on or after September 10, 2026, now retain instance state for seven days by default instead of 30 days.
Use Cloudflare Containers with Codex via the OpenAI Agents API
Sep 10, 2026
· release notes
Cloudflare Containers now supports self-hosted execution environments for the OpenAI Agents API via an open-source Worker template.
Adds support for running Cloudflare Containers as the execution environment for the OpenAI Agents API, enabling self-hosted Codex sessions.
1 detail in Everything
Cloudflare: Raises the uncompressed Worker bundle size limit to 64 MiB for all plans (free and paid), replacing the old compressed-size limits of 3 MB (Free) and 10 MB (Paid); use wrangler deploy --outdir bundled/ --dry-run to check bundle size before deploying.
└──▷ TRY IT
Check your Worker's uncompressed bundle size before deploying to confirm it is within the new 64 MiB limit.
copy
$ wrangler deploy --outdir bundled/ --dry-run Serve a Django app from a Python Worker using the new WSGI WSGI A Python standard (PEP 3333) defining how a web server passes HTTP requests to a Python application, letting frameworks and servers interoperate without custom glue code.
python
copy
from workers import wsgi
from django.core.wsgi import get_wsgi_application
app = get_wsgi_application()
Default = wsgi.entrypoint(app)
Adds .signedUrl() , .createDirectUpload() , and filter.metadata to the Images binding for server-side signing, direct creator uploads, and metadata-filtered image listing. Adds headers option to .response() in the Images binding to set response headers (including Cache-Control ) in a single call. Supports bulk creation of multiple Cloudflare Tunnel and Cloudflare Mesh routes in a single action from the Routes UI, including comma-separated CIDR CIDR A notation for a block of IP addresses, such as 10.0.0.0/24. The number after the slash says how many leading address bits identify the network. Add another staging. Adds Source subnets field for matching traffic by source IP range when defining custom applications for breakout and prioritized traffic on the Cloudflare One Appliance dashboard. Upgrades Python Workers to Python 3.14 (Pyodide runtime 314.0.6) by default for all new workers using the corresponding compatibility date.
+3 more
show less
Releases Miniflare v5 with a new configuration shape aligned to cloudflare.config.ts to prepare local Workers development for the upcoming cf CLI. Adds support for running Cursor Cloud Agents on Cloudflare via self-hosted machines backed by Cloudflare Containers, using the open-source Cursor Cloudflare Workers template. Extends Radar search to include Internet events and outages alongside existing results, with event links that preserve date ranges; results are also available to browser-based AI agents via WebMCP.
Adds .signedUrl() , .createDirectUpload() , and filter.metadata to the Images binding for server-side signing, direct creator uploads, and metadata-filtered image listing. Adds headers option to .response() in the Images binding to set response headers (including Cache-Control ) in a single call. Adds Source subnets field for matching traffic by source IP range when defining custom applications for breakout and prioritized traffic on the Cloudflare One Appliance dashboard. Adds support for running Cursor Cloud Agents on Cloudflare via self-hosted machines backed by Cloudflare Containers, using the open-source Cursor Cloudflare Workers template.
4 more in Everything
└──▷ BREAKING ON UPGRADE
! Miniflare v5 removes deprecated APIs and options, including legacy alpha D1 bindings.! Miniflare v5 removes internal APIs such as wrappedBindings.! Miniflare v5 removes built-in module discovery; the module graph must now be provided by higher-level tools like Wrangler or the Vite plugin.! Miniflare v5 moves local-only /cdn-cgi routes under /cdn-cgi/local.! Miniflare v5 replaces per-resource persistence options with shared persistence root options.
Cloudflare API v7.10.0 adds billing management, payment methods, field extractors, and Spectrum analytics endpoints
└──▷ TRY IT
Retrieve unpaid invoices for an account to drive automated dunning or alerting workflows.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/accounts/{account_id}/billing/unpaid-invoice' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' Download a receipt as a PDF for record-keeping or auditing after a payment is confirmed.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/accounts/{account_id}/receipts/{receipt_id}/pdf' \
-H 'Authorization: Bearer <API_TOKEN>' \
--output receipt.pdf Pull a Spectrum bandwidth report to investigate DDoS DDoS Distributed Denial of Service: an attack that floods a target system with traffic from many sources simultaneously, exhausting its resources so legitimate requests cannot be served.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/user/spectrum_analytics/zones/report' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json'
Adds POST /accounts/{account_id}/subscriptions/cancel-downgrade to cancel a delayed subscription downgrade. Adds POST /accounts/{account_id}/subscriptions/{subscription_identifier}/cancel-reason and GET /accounts/{account_id}/subscriptions/{subscription_identifier}/cancel-reason to create and retrieve subscription cancel reasons. Adds POST /accounts/{account_id}/subscriptions/{subscription_identifier}/action/append to append actions to a subscription. Adds POST /accounts/{account_id}/bulk/subscriptions for bulk subscription creation. Adds full payment method CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. GET/POST /accounts/{account_id}/payment-methods, GET/PUT/DELETE /accounts/{account_id}/payment-methods/{payment_method_id}, and POST /accounts/{account_id}/payment-methods/{payment_method_id}/set-as-default.
+16 more
show less
Adds POST /accounts/{account_id}/pay-invoice to pay an invoice programmatically. Adds POST /accounts/{account_id}/pay-bad-debt to pay account bad debt. Adds GET /accounts/{account_id}/receipts/{receipt_id}/pdf to retrieve a receipt as a PDF. Adds POST /accounts/{account_id}/invoices to toggle PDF invoices. Adds POST /accounts/{account_id}/client-secret to create a Stripe setup intent client secret. Adds GET /user/spectrum_analytics/zones/report to retrieve a zones bandwidth report via Spectrum Analytics. Adds GET /zones/{zone_id}/spectrum/protocols to list supported Spectrum application protocols. Adds POST /billing/address-validation to validate a billing address. Adds POST /accounts/{account_id}/billing/profile/payment-method to create a payment intent for a billing profile. Adds GET /accounts/{account_id}/billing/credits to retrieve account credits. Adds GET /accounts/{account_id}/billing/history to retrieve account billing history. Adds GET /accounts/{account_id}/billing/bad-debt to retrieve account bad debt. Adds GET /accounts/{account_id}/billing/unpaid-invoice to list unpaid invoices. Adds GET /billing/rate_plans/{public_key} to retrieve a rate plan by public key. Adds GET/PUT/DELETE /accounts/{account_id}/field_extractors/{extractor} endpoints to manage field extractors. Bumps the cloudflare-go SDK to v7.10.0 via go get -u github.com/cloudflare/cloudflare-go/v7@v7.10.0.
Adds POST /accounts/{account_id}/subscriptions/cancel-downgrade to cancel a delayed subscription downgrade. Adds POST /accounts/{account_id}/subscriptions/{subscription_identifier}/cancel-reason and GET /accounts/{account_id}/subscriptions/{subscription_identifier}/cancel-reason to create and retrieve subscription cancel reasons. Adds POST /accounts/{account_id}/subscriptions/{subscription_identifier}/action/append to append actions to a subscription. Adds POST /accounts/{account_id}/bulk/subscriptions for bulk subscription creation. Adds full payment method CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. GET/POST /accounts/{account_id}/payment-methods, GET/PUT/DELETE /accounts/{account_id}/payment-methods/{payment_method_id}, and POST /accounts/{account_id}/payment-methods/{payment_method_id}/set-as-default.
+15 more
show less
Adds POST /accounts/{account_id}/pay-invoice to pay an invoice programmatically. Adds POST /accounts/{account_id}/pay-bad-debt to pay account bad debt. Adds GET /accounts/{account_id}/receipts/{receipt_id}/pdf to retrieve a receipt as a PDF. Adds POST /accounts/{account_id}/invoices to toggle PDF invoices. Adds POST /accounts/{account_id}/client-secret to create a Stripe setup intent client secret. Adds GET /user/spectrum_analytics/zones/report to retrieve a zones bandwidth report via Spectrum Analytics. Adds GET /zones/{zone_id}/spectrum/protocols to list supported Spectrum application protocols. Adds POST /billing/address-validation to validate a billing address. Adds POST /accounts/{account_id}/billing/profile/payment-method to create a payment intent for a billing profile. Adds GET /accounts/{account_id}/billing/credits to retrieve account credits. Adds GET /accounts/{account_id}/billing/history to retrieve account billing history. Adds GET /accounts/{account_id}/billing/bad-debt to retrieve account bad debt. Adds GET /accounts/{account_id}/billing/unpaid-invoice to list unpaid invoices. Adds GET /billing/rate_plans/{public_key} to retrieve a rate plan by public key. Adds GET/PUT/DELETE /accounts/{account_id}/field_extractors/{extractor} endpoints to manage field extractors.
1 more in Everything
Cloudflare adds Python 3.14 Workers, 64 MiB bundle limits, Radar event search, and One Appliance dashboard controls
Supports Python 3.14 runtime for Python Workers. Raises the uncompressed Worker bundle size limit to 64 MiB for all plans (free and paid), removing the previous compressed-size caps of 3 MB and 10 MB. Adds Internet events and outages to Cloudflare Radar search, with links to relevant pages and historical context. Enables creation, editing, and deletion of custom applications for Cloudflare One Appliance from the dashboard, matched by hostname, IP subnet, or source subnet. Adds the ability to configure custom DHCP options on a LAN's DHCP server directly from the Cloudflare One Appliance dashboard, without requiring API or Terraform.
Enables creation, editing, and deletion of custom applications for Cloudflare One Appliance from the dashboard, matched by hostname, IP subnet, or source subnet. Adds the ability to configure custom DHCP options on a LAN's DHCP server directly from the Cloudflare One Appliance dashboard, without requiring API or Terraform.
3 more in Everything
Cloudflare adds 64 MiB Workers bundles, Python 3.14 support, Radar Internet events search, and One Appliance custom apps and DHCP options
└──▷ HOW TO FIND IT
Investigate an outage or Internet disruption event directly from Radar search to get historical context and relevant pages.
📍 Navigate to Cloudflare Radar (radar.cloudflare.com) and type a country, ASN, or region name into the search bar — results now include Internet events and outages alongside routing and traffic data.
Route breakout or prioritized traffic for a specific SaaS SaaS Software delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally.
📍 In the Cloudflare One Appliance dashboard, go to Applications › Create application, enter a hostname, IP subnet, or source subnet to match, choose breakout or prioritized traffic mode, then save.
Cloudflare Radar search now includes Internet events and outages, with links to relevant pages and historical context.
1 more in Everything
New CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic.
Cloudflare One Client for macOS (version 2026.8.1290.1)
Sep 9, 2026
· release notes
Cloudflare One Client for macOS adds non-RFC1918 RFC1918 IETF standard that reserves three IPv4 address ranges (10.x, 172.16–31.x, 192.168.x) for private networks, never routed on the public internet, giving tools a reliable way to identify internal traffic.
Added support for routing non-RFC 1918 local IPv4 networks through the WARP tunnel when unrestricted LAN inclusion is enabled by policy or MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies. Improved DNS reliability on networks with lower MTUs by clamping the TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. DNS-over-HTTPS DNS-over-HTTPS A protocol that tunnels DNS queries inside encrypted HTTPS requests, hiding lookups from network observers. Cyber tools use it to evade DNS-based monitoring or filtering.
2 details in Everything
Cloudflare One Client for Windows (version 2026.8.1290.1)
Sep 9, 2026
· release notes
Adds unrestricted LAN inclusion for non-RFC 1918 RFC 1918 IETF standard that reserves three IPv4 address ranges (10.x, 172.16–31.x, 192.168.x) for private networks, never routed on the public internet, giving tools a reliable way to identify internal traffic.
Adds support for routing non-RFC 1918 local IPv4 networks through the WARP tunnel when unrestricted LAN inclusion is enabled by policy or MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies. Implements a service recovery mechanism backed by Windows scheduler task to start WARP service on system unlock if not already started. Removes the requirement for the Windows WLAN AutoConfig service to be running.
3 details in Everything
Cloudflare adds 64 MiB Worker bundles, WSGI WSGI A Python standard (PEP 3333) defining how a web server passes HTTP requests to a Python application, letting frameworks and servers interoperate without custom glue code. ASGI ASGI A Python async web server interface specification that defines how servers and applications exchange HTTP and WebSocket messages; cyber tools use it to serve high-concurrency APIs without blocking on I/O.
└──▷ TRY IT
Check a Worker's uncompressed bundle size against the 64 MiB limit before deploying to catch oversized builds in CI without actually publishing.
copy
$ wrangler deploy --outdir bundled/ --dry-run Run a Django app inside a Python Worker by wiring Django's WSGI application into the Workers runtime entry point.
python
copy
from workers import wsgi
from django.core.wsgi import get_wsgi_application
app = get_wsgi_application()
Default = wsgi.entrypoint(app)
Add a source-subnet match to a custom breakout application on Cloudflare One Appliance so that traffic from a specific internal IP range is steered without an API call.
📍 In the Cloudflare One Appliance dashboard, go to Traffic Steering › Breakout traffic, select Assign application traffic › Add, enter hostnames or IP subnets, then set Source subnets to your internal CIDR range (e.g. 10.10.0.0/24) and save.
Adds --outdir and --dry-run flags to wrangler deploy to inspect uncompressed bundle size before deploying, now checked against a unified 64 MiB limit across Free and Paid plans (previously 3 MB / 10 MB compressed) Adds wsgi.entrypoint() and asgi.entrypoint() from the workers module to support WSGI frameworks (Django, Flask) and ASGI frameworks (FastAPI, Starlette) in Python Workers Adds .text() method to the Images binding to rasterize text into or over an image, with font, size, and color style options; also adds a text key to the draw array in cf.image Adds filter.metadata parameter to .list() in the Images binding to filter hosted images by custom metadata, including bounded range conditions (e.g., priority: { gte: 2, lte: 5 }) Adds .signedUrl() to the Images binding to generate signed URLs for private hosted images server-side
+8 more
show less
Adds .createDirectUpload() to the Images binding to create Direct Creator Upload links for client-side image uploads Adds headers option to .response() in the Images binding to set response headers in a single call; Content-Type is always taken from the optimized image and cannot be overridden Adds Source subnets field in Traffic Steering (Breakout traffic / Prioritized traffic) on the Cloudflare One Appliance dashboard to match traffic by source IP range when defining custom applications Enables defining and editing custom applications for breakout and prioritized traffic directly from the Cloudflare One Appliance dashboard under Traffic Steering, without calling the API Enables configuring custom DHCP options (PXE/iPXE boot, VoIP provisioning, vendor-specific, or arbitrary option code/type/value) from the Cloudflare One Appliance dashboard under LAN configuration > DHCP server options Supports bulk creation of Cloudflare Tunnel and Cloudflare Mesh routes in a single action: comma-separated CIDR CIDR A notation for a block of IP addresses, such as 10.0.0.0/24. The number after the slash says how many leading address bits identify the network. Add another staging, and automatic removal of successfully created routes on partial failure Adds Cursor self-hosted machines integration, running Cursor Cloud Agents on Cloudflare Containers with a Durable Object namespace, R2 bucket binding, and cron trigger via the open-source Cursor Cloudflare Workers template Refreshes Log Explorer dataset configuration with grouped field selection (with per-category counts), field data-type details, bulk select/reset controls, and ingestion filters accessible via Add dataset or Actions > Edit
Adds wsgi.entrypoint() and asgi.entrypoint() from the workers module to support WSGI frameworks (Django, Flask) and ASGI frameworks (FastAPI, Starlette) in Python Workers Adds .text() method to the Images binding to rasterize text into or over an image, with font, size, and color style options; also adds a text key to the draw array in cf.image Adds filter.metadata parameter to .list() in the Images binding to filter hosted images by custom metadata, including bounded range conditions (e.g., priority: { gte: 2, lte: 5 }) Adds .signedUrl() to the Images binding to generate signed URLs for private hosted images server-side Adds .createDirectUpload() to the Images binding to create Direct Creator Upload links for client-side image uploads
+3 more
show less
Adds headers option to .response() in the Images binding to set response headers in a single call; Content-Type is always taken from the optimized image and cannot be overridden Adds Source subnets field in Traffic Steering (Breakout traffic / Prioritized traffic) on the Cloudflare One Appliance dashboard to match traffic by source IP range when defining custom applications Adds Cursor self-hosted machines integration, running Cursor Cloud Agents on Cloudflare Containers with a Durable Object namespace, R2 bucket binding, and cron trigger via the open-source Cursor Cloudflare Workers template
5 more in Everything
Radar search now includes Internet events
Sep 8, 2026
· release notes
Radar search now includes Internet events and outages alongside existing results
Enables searching event descriptions and related entities (locations, ASes, bots, TLDs) Event links preserve the event date range for investigation
2 details in Everything
Miniflare v5 prepares local development for the cf CLI
Sep 8, 2026
· release notes
Miniflare v5 refactors configuration for cf CLI alignment; removes legacy APIs and moves routes.
└──▷ BREAKING ON UPGRADE
! Removed deprecated APIs and options, such as legacy alpha D1 bindings! Removed internal APIs like wrappedBindings! Moved local-only /cdn-cgi routes under /cdn-cgi/local! Replaced per-resource persistence options with shared persistence root options
Configure observability per container application
Sep 8, 2026
· release notes
Wrangler adds per-container observability configuration with instance targeting for Workers
Adds containers[].observability config section in Wrangler to override top-level settings per container Adds target_instance_percentage and target_instance_count fields within containers[].observability to scope logging to a subset of instances Enables omitting containers[].observability to inherit the top-level observability setting for a container
3 details in Everything
API surface changed: 15 modified
API change API surface changed: 15 modified
~ DELETE /accounts/{account_id}/devices/networks/{network_id}: request body changed ~ DELETE /accounts/{account_id}/devices/policy/{policy_id}: request body changed ~ DELETE /accounts/{account_id}/devices/posture/integration/{integration_id}: request body changed ~ DELETE /accounts/{account_id}/devices/posture/{rule_id}: request body changed ~ DELETE /accounts/{account_id}/event_subscriptions/subscriptions/{subscription_id}: response schema changed ~ GET /accounts/{account_id}/artifacts/namespaces/{namespace}/repos: response schema changed ~ GET /accounts/{account_id}/artifacts/namespaces/{namespace}/repos/{name}: response schema changed ~ GET /accounts/{account_id}/cloudforce-one/events/dataset/{dataset_id}/indicators: response schema changed ~ GET /accounts/{account_id}/cloudforce-one/events/indicators: response schema changed ~ GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles: param article_id (query) added ~ POST /accounts/{account_id}/artifacts/namespaces/{namespace}/repos: response schema changed ~ POST /accounts/{account_id}/artifacts/namespaces/{namespace}/repos/{name}/fork: response schema changed ~ POST /accounts/{account_id}/artifacts/namespaces/{namespace}/repos/{name}/import: response schema changed ~ POST /accounts/{account_id}/cloudforce-one/events/create: request body changed ~ POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/tag: response schema changed
DELETE /accounts/{account_id}/devices/networks/{network_id}: request body changed DELETE /accounts/{account_id}/devices/policy/{policy_id}: request body changed DELETE /accounts/{account_id}/devices/posture/integration/{integration_id}: request body changed DELETE /accounts/{account_id}/devices/posture/{rule_id}: request body changed DELETE /accounts/{account_id}/event_subscriptions/subscriptions/{subscription_id}: response schema changed
+10 more
show less
GET /accounts/{account_id}/artifacts/namespaces/{namespace}/repos: response schema changed GET /accounts/{account_id}/artifacts/namespaces/{namespace}/repos/{name}: response schema changed GET /accounts/{account_id}/cloudforce-one/events/dataset/{dataset_id}/indicators: response schema changed GET /accounts/{account_id}/cloudforce-one/events/indicators: response schema changed GET /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles: param article_id (query) added POST /accounts/{account_id}/artifacts/namespaces/{namespace}/repos: response schema changed POST /accounts/{account_id}/artifacts/namespaces/{namespace}/repos/{name}/fork: response schema changed POST /accounts/{account_id}/artifacts/namespaces/{namespace}/repos/{name}/import: response schema changed POST /accounts/{account_id}/cloudforce-one/events/create: request body changed POST /accounts/{account_id}/cloudforce-one/v2/threat-signals/articles/{article_id}/tag: response schema changed
15 details in Everything
WAF - Attack Signature Detection is now available in Early Access (2026-09-07)
Sep 7, 2026
·
issue 092
Attack Signature Detection (Early Access) adds passive WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
New detection Adds Attack Signature Detection (Early Access), which evaluates requests against Cloudflare attack signatures and records matches without applying a mitigation action, so you can investigate detected traffic before deciding how to respond.Surfaces matched signature references, categories, confidence levels, and request outcomes in Security Analytics > Attack Analysis for pre-mitigation review. Enables use of Attack Signature Detection fields in Security Rules, combinable with request properties such as hostname, path, and HTTP method, to apply scoped mitigation after investigation.
3 details in Everything
WAF - Enforce positive security with Application Profiles (2026-09-07)
Sep 7, 2026
·
issue 081
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ HOW TO FIND IT
Review Schema Profile conformance trends and violation samples in Security Analytics before committing to enforcement.
📍 In the Cloudflare dashboard, go to Security › Analytics › Profile Analysis to inspect conformance trends and sampled non-conforming requests for your Schema Profile.
Introduces Application Profiles, a new positive-security layer for Cloudflare WAF that learns expected request structure and classifies traffic as conforming or non-conforming without blocking.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Schema Profiles as the first profile type, modeling path variables, query parameters, headers, cookies, JSON bodies, and form-encoded bodies — including field types, numeric ranges, string lengths, and character classes. Adds Profile Analysis view in Security Analytics to review conformance trends and sampled violation details before enforcing a profile. Enables enforcement of Application Profiles via Custom Rules, allowing scope by hostname, path, operation, or other security signals such as Attack Score.
4 details in Everything
API surface changed: +42 endpoints, −1 endpoint, 421 modified
460 details in Everything
└──▷ BREAKING ON UPGRADE
! Removed endpoint POST /accounts/{account_id}/realtime/kit/{app_id}/livestreams! GET /accounts/{account_id}/email-security/settings/domains/{domain_id}/verification: response schema changed! POST /accounts/{account_id}/access/organizations/revoke_user: request body changed; response schema changed! POST /zones/{zone_id}/access/organizations/revoke_user: request body changed; response schema changed
Deploy larger Workers — up to 64 MiB for both free and paid plans
Sep 4, 2026
· release notes
Cloudflare increases Workers bundle size limit from 3 MiB/10 MB to 64 Mi uncompressed for all plans.
Uncompressed bundle limit raised to 64 MiB across Free and Paid plans, replacing previous 3 MB (Free) and 10 MB (Paid) limits.
1 detail in Everything
R2 now exposes asynchronous, best-effort Data Access Logs for object operations, integrated with Workers Observability filtering by bucket, operation, interface, and actor.
Manage Email Routing rules with Wrangler
Sep 4, 2026
· release notes
Wrangler now supports managing Email Routing addresses via the top-level addresses field in wrangler.toml
Adds support for the addresses config key in wrangler.toml to declaratively manage Email Routing rules Automates creation, update, and removal of Email Routing rules during wrangler deploy
2 details in Everything
Enterprise customers can self-serve CDN upload limits up to 5 GB
Sep 4, 2026
· release notes
Enterprise customers can self-serve CDN CDN A content delivery network, servers distributed across locations that cache and serve content near readers. It can reduce loading time and traffic to the original server.
Cloudflare Workers AI adds three new models: Claude Fable 5.1, GLM-5.3, and GLM-5.3 Flash GLM-5.3 Flash A lightweight, fast large language model in Zhipu AI's GLM family, designed for low-latency inference, making it useful for cyber tools that need embedded AI reasoning without heavy compute overhead.
Adds claude-fable-5.1 (Anthropic) with a 1M-token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. Adds glm-5.3 (Z.ai) with a 1M-token context window, reasoning, function calling function calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions. structured outputs structured outputs Forcing a model's response to match a given format or JSON schema, so software can parse it reliably instead of hoping the text is well formed. Adds glm-5.3-flash (Z.ai), a natively multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats.
3 details in Everything
Cloudflare adds new Workers AI models, Log Explorer dataset deletion, crawl Content Signals support, and Access token Access token A credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions.
└──▷ TRY IT
Crawl a page for reference-only use, so the request is rejected if the site's robots.txt permits less than reference level access.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/{account_id}/browser-rendering/crawl' \
-H 'Authorization: Bearer <apiToken>' \
-H 'Content-Type: application/json' \
-d '{"url": "https://example.com", "contentUse": "reference", "formats": ["markdown"]}'
Adds contentUse parameter to the /crawl endpoint (POST https://api.cloudflare.com/client/v4/accounts/{account_id}/browser-rendering/crawl) supporting values reference, full (default); requests are rejected with a 400 error when a target site's robots.txt sets a more restrictive use level. Adds deletion_protection field to Log Explorer dataset management — set it to false via the Update an account or zone dataset API method before calling Delete an account or zone dataset to permanently remove account or zone datasets. Access service token Client Secrets created on or after August 26, 2026 use the new scannable format cfast_[40 alphanumeric characters][8-character checksum], compatible with existing CF-Access-Client-Id / CF-Access-Client-Secret headers and secret scanning secret scanning Checking files, code or other data for exposed credentials such as passwords, API keys and tokens. Findings help teams remove the secret and revoke or rotate it. Adds @cf/zai-org/glm-5.3 to Workers AI — Z.ai's flagship agentic coding model at $1.40/M input tokens, $0.26/M cached input tokens, $4.40/M output tokens; accessible via Workers AI binding (env.AI.run() ), REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Adds @cf/zai-org/glm-5.3-flash to Workers AI — first natively multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. Mixture-of-Experts Mixture-of-Experts A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token.
+7 more
show less
AI Search now supports @cf/zai-org/glm-5.3-flash for text generation with a 1,048,576-token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. AI Search adds six new text generation models: @cf/deepseek-ai/deepseek-v4-flash-0731 (1,048,576-token context), @cf/deepseek-ai/deepseek-v4-pro-0813 (1,048,576), @cf/openai/gpt-oss-120b (128,000), @cf/openai/gpt-oss-20b (128,000), @cf/qwen/qwen3.8-27b (262,144), and @cf/moonshotai/kimi-k2.7-code (262,144); all run on Workers AI without an additional provider key. Durable Objects can now use up to ten distinct Dynamic Workers with in-flight requests concurrently, up from four. Log Explorer adds a refreshed dataset configuration UI with grouped field selection, field-level data type details, bulk select/reset controls, and ingestion filters — accessible via Add dataset or Actions > Edit for an enabled dataset. Radar Researcher beta adds connected insights linking to Radar pages, reports, and blog posts; an Explain with AI button on URL Scanner reports; and fullscreen shared conversation sessions. D1 now enforces free tier daily row read and row write limits on the Workers Free plan starting September 1, 2026 — queries via the Workers Binding API and REST API return explicit error messages when limits are exceeded; limits reset at midnight UTC. Enterprise customers must migrate from the Azure Functions-based Microsoft Sentinel connector to the Cloudflare for Microsoft Sentinel Codeless Connector Framework (CCF) connector by 2026-09-14.
12 details in Everything
└──▷ BREAKING ON UPGRADE
! The Azure Functions-based Microsoft Sentinel Logpush connector stops working after 2026-09-14 when Microsoft retires the Azure Monitor HTTP Data Collector API; migration to the CCF connector is required.! D1 queries on the Workers Free plan fail (with row read or row write limit errors) once daily limits are exceeded, beginning September 1, 2026.! AI Gateway monthly usage invoices no longer include separate input/output token quantities and unit prices; each model now appears as a single cost line item using a standardized provider/model identifier format (e.g. anthropic/claude-haiku-4.5).
Cloudflare API adds email security batch operations, browser rendering live view, and SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination.
└──▷ TRY IT
Get an SSL/TLS configuration recommendation for a zone to identify upgrade opportunities or misconfigurations.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/zones/<zone_id>/ssl/recommendation' \
-H 'Authorization: Bearer <API_TOKEN>' Mint a live-view URL to observe or debug an active browser rendering session in real time.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/<account_id>/browser-rendering/devtools/browser/<session_id>/live_view' \
-H 'Authorization: Bearer <API_TOKEN>'
Adds POST /accounts/{account_id}/email-security/settings/allow_policies/batch for batch allow-policy operations in Email Security. Adds POST /accounts/{account_id}/email-security/settings/block_senders/batch for batch blocked-sender operations in Email Security. Adds POST /accounts/{account_id}/email-security/settings/domains/batch for batch email domain operations in Email Security. Adds POST /accounts/{account_id}/email-security/settings/trusted_domains/batch for batch trusted-domain operations in Email Security. Adds endpoints to add a new email domain and replace an existing email domain in Email Security settings.
+3 more
show less
Adds endpoint to replace a preset in Email Security settings. Adds /zones/{zone_id}/ssl/recommendation endpoint to retrieve SSL/TLS configuration recommendations for a zone. Adds /accounts/{account_id}/browser-rendering/devtools/browser/{session_id}/live_view endpoint to mint live-view URLs for an active browser rendering session.
8 details in Everything
AI Gateway invoice consolidation, D1 free-tier query limits enforced, new /crawl contentUse param, and GLM-5.3 Flash GLM-5.3 Flash A lightweight, fast large language model in Zhipu AI's GLM family, designed for low-latency inference, making it useful for cyber tools that need embedded AI reasoning without heavy compute overhead.
Adds contentUse parameter to the /crawl endpoint so crawl requests enforce the use directive declared in a site's robots.txt Content Signals. AI Search now supports the Workers AI GLM-5.3 Flash model for text generation. D1 now enforces daily row read and row write limits on Workers Free accounts — queries exceeding the limit fail with an error. AI Gateway monthly usage invoices now display total cost per model and standardize model names across invoices and logs.
4 details in Everything
└──▷ BREAKING ON UPGRADE
! D1 queries on Workers Free accounts that exceed daily row read or row write limits will fail and return errors beginning September 1, 2026.
Cloudflare: Cloudflare One Client version 2026.7.1376.0 released for macOS and Windows.
└──▷ BREAKING ON UPGRADE
! D1 queries on Workers Free accounts that exceed daily row read or row write limits now fail and return errors (enforced from September 1, 2026).
Cursor Cloud Agents can now run inside customer-controlled Cloudflare Sandbox environments via Cursor Self-Hosted Machines.
Supports running Cursor Cloud Agents on Cloudflare Sandboxes as a self-hosted worker, keeping tool calls (terminal, filesystem, browser actions) inside the customer's Cloudflare account rather than on Cursor-managed infrastructure. Supports Cursor self-hosted worker pools as named routing targets, allowing new agent chats to queue until an available worker claims them, with pool orchestration to scale capacity on demand. Exposes a Cloud Agents API for integrating self-hosted machine status and pool routing into external systems. Uses an outbound-only connectivity model: the Cursor worker opens a long-lived outbound HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate. Supports individual developer use via My Machines for connecting a single worker, alongside enterprise team pool configurations.
+1 more
show less
Extends Cloudflare Sandboxes' agent platform support to include Cursor Cloud Agents, alongside the previously announced Devin Outposts and Claude Managed Agents integrations.
6 details in Everything
New in Images: text rasterization and updates to the binding
Sep 2, 2026
· release notes
Cloudflare Images binding adds text rasterization, signed URLs, direct uploads, and metadata filtering
Adds .text() method to rasterize text into images using font, size, and color options Updates cf.image.draw array to accept a text key for drawing text overlays Adds filter.metadata parameter to .list() for filtering hosted images by custom metadata including range queries Adds .signedUrl() method to generate signed URLs for private hosted images Adds .createDirectUpload() method to create Direct Creator Upload links for client-side uploads
+1 more
show less
Updates .response() to accept a headers option for setting response headers without rebuilding the Response object
6 details in Everything
Define custom applications for breakout and prioritized traffic from the Cloudflare One Appliance dashboard
Sep 2, 2026
· release notes
Cloudflare One Appliance adds dashboard UI for defining custom breakout and prioritized traffic applications with new Source subnets field
Adds ability to define custom applications for breakout and prioritized traffic directly from the Cloudflare One Appliance dashboard without calling the API Adds Source subnets field to custom application rules, allowing traffic matching by source IP range in addition to Hostnames and IP subnets
2 details in Everything
Configure DHCP options from the dashboard on Cloudflare One Appliance
Sep 2, 2026
· release notes
Cloudflare One Appliance now supports configuring custom DHCP options directly from the dashboard UI.
Configure Origin Range Requests with the Rulesets API
Sep 2, 2026
· release notes
Cloudflare adds origin_range_requests mode to Cache Rules via the Rulesets API for byte-range fetching
Run Cursor Cloud Agents on Cloudflare via self-hosted machines
Sep 2, 2026
· release notes
Enables running Cursor Cloud Agents on Cloudflare infrastructure using self-hosted machines.
Python Workers now support WSGI web frameworks like Django and Flask
Sep 2, 2026
· release notes
Python Workers now support WSGI WSGI A Python standard (PEP 3333) defining how a web server passes HTTP requests to a Python application, letting frameworks and servers interoperate without custom glue code. ASGI ASGI A Python async web server interface specification that defines how servers and applications exchange HTTP and WebSocket messages; cyber tools use it to serve high-concurrency APIs without blocking on I/O.
└──▷ USE IT
Deploy a Django application on Cloudflare Workers by importing the new WSGI helper and wrapping the standard Django app object.
code
copy
from workers import wsgi
from django.core.wsgi import get_wsgi_application
app = get_wsgi_application()
Default = wsgi.entrypoint(app)
Deploy a FastAPI application on Cloudflare Workers by importing the new ASGI helper and wrapping the standard FastAPI app object.
code
copy
from workers import asgi
from fastapi import FastAPI
app = FastAPI()
Default = asgi.entrypoint(app)
Adds workers.wsgi.entrypoint function for creating Worker entry points from WSGI applications. Adds workers.asgi.entrypoint function for creating Worker entry points from ASGI applications.
2 details in Everything
Create multiple Cloudflare Tunnel and Cloudflare Mesh routes at once
Sep 2, 2026
· release notes
Bulk create Cloudflare Tunnel and Mesh routes from the UI with comma-separated lists or queued entries.
Adds comma-separated destination input to create multiple routes of the same type in one action Adds Add another button to queue multiple distinct routes (different types/connectors) before creating them together Automatically removes successfully created routes from the form on partial failure, isolating failed entries for retry
3 details in Everything
Cloudflare adds Content Signals crawl controls, new Workers AI models, symmetric JWT JWT An open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object passed between parties. Cyber tools use it to verify identity and permissions without querying a central session store. MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Access token Access token A credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions.
└──▷ TRY IT
Crawl a page for reference-only use, so the request is rejected if the site's robots.txt restricts content to below reference level.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/{account_id}/browser-rendering/crawl' \
-H 'Authorization: Bearer <apiToken>' \
-H 'Content-Type: application/json' \
-d '{"url": "https://example.com", "contentUse": "reference", "formats": ["markdown"]}' Temporarily disable a suspected-compromised Access service token without deleting it, preserving config for later re-enabling.
📍 Settings › Access › Service Tokens › select token › Toggle Enabled to off ('Turn a service token on or off')
Adds contentUse parameter to the POST /client/v4/accounts/{account_id}/browser-rendering/crawl endpoint, accepting values reference or full (default), to enforce Content Signals use directives from a target site's robots.txt; requests are rejected with a 400 if the site's declared level is more restrictive than contentUse. MCP server portal /mcp endpoint now accepts stateless MCP 2026-07-28 requests alongside earlier 2025 Streamable HTTP Streamable HTTP An MCP transport protocol that lets a client send JSON-RPC requests over HTTP POST while the server streams responses back using Server-Sent Events, replacing the older stdio and SSE transports for remote tool communication. SSE SSE Server-Sent Events, a browser API and HTTP-based protocol where a server pushes a stream of text events to a client over a single long-lived connection, giving tools a lightweight alternative to WebSockets for one-way real-time updates. Durable Objects can now have up to ten concurrent in-flight Dynamic Workers (increased from four), with the limit shared across all concurrent requests to the same Durable Object. Adds @cf/zai-org/glm-5.3-flash (first multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. MoE MoE A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token. AI Search gains six additional Workers AI text-generation models: @cf/openai/gpt-oss-120b (128,000-token context), @cf/openai/gpt-oss-20b (128,000-token context), @cf/moonshotai/kimi-k2.7-code (262,144-token context), and three others; no additional provider key required.
+4 more
show less
Cloudflare Access administrators can now set a grace period (1 hour to 30 days, or a custom RFC 3339 expiration via the API) when rotating a service token secret, keeping both secrets valid during the transition. Cloudflare Access administrators can now temporarily disable service tokens without deleting them; a disabled token cannot authenticate but its configuration is preserved for re-enabling. App-scoped API tokens for Flagship are now available, granting access only to selected Flagship apps with Evaluate , Read , or Write Flagship App permissions, selectable via the Specified Flagship apps option in the resource dropdown when creating a custom token. Radar Researcher responses can now link to relevant Radar pages, reports, and Cloudflare Blog posts, and the Explain with AI button on URL Scanner reports enables AI-driven explanation of scan findings with follow-up Q&A.
9 details in Everything
└──▷ BREAKING ON UPGRADE
! The Azure Functions-based Microsoft Sentinel Logpush connector stops being maintained after 2026-09-14 when Microsoft retires the Azure Monitor HTTP Data Collector API; affected Enterprise customers must migrate to the Cloudflare for Microsoft Sentinel Codeless Connector Framework (CCF) connector before that date.
Cloudflare adds GLM-5.3 models, Durable Object alarm control, JWT JWT An open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object passed between parties. Cyber tools use it to verify identity and permissions without querying a central session store. Access token Access token A credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions.
└──▷ USE IT
Prevent a one-shot cleanup alarm from retrying after it aborts the Durable Object.
src/index.js
copy
this.ctx.abort("Cleanup complete", { retryAlarm: false });
Adds { retryAlarm: false } option to ctx.abort() in Durable Objects, preventing alarm retries after the object resets — useful for one-shot cleanup alarms. JWT validation now supports symmetric HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it. HS256, HS384, and HS512 algorithms, configurable via the Cloudflare dashboard or API. Adds grace period option when rotating Access service token secrets (1 hour to 30 days via dashboard; RFC 3339 expiration time via API), keeping both secrets valid during the window. Adds ability to temporarily disable Access service tokens without deleting them, stopping authentication and any active rotation grace period. MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. /mcp endpoint now accepts stateless MCP 2026-07-28 specification requests alongside earlier 2025 Streamable HTTP Streamable HTTP An MCP transport protocol that lets a client send JSON-RPC requests over HTTP POST while the server streams responses back using Server-Sent Events, replacing the older stdio and SSE transports for remote tool communication.
+5 more
show less
Durable Objects can now have up to ten concurrent in-flight Dynamic Workers (increased from four); other Workers retain a limit of four per request. Adds @cf/zai-org/glm-5.3 (agentic coding model) to Workers AI at $1.40/M input tokens, $0.26/M cached input tokens, $4.40/M output tokens. Adds @cf/zai-org/glm-5.3-flash (multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. Mixture-of-Experts Mixture-of-Experts A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token. AI Search adds six new Workers AI text generation models including @cf/openai/gpt-oss-120b (128K context), @cf/openai/gpt-oss-20b (128K context), @cf/moonshotai/kimi-k2.7-code (262K context), and others with up to 1,048,576-token context windows context windows The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. Flagship API tokens can now be scoped to specific apps by selecting Specified Flagship apps in the resource dropdown and assigning Evaluate, Read, or Write permissions per app.
10 details in Everything
└──▷ BREAKING ON UPGRADE
! The Azure Functions-based Microsoft Sentinel Logpush connector will stop working after 2026-09-14 (when Microsoft deprecates the Azure Monitor HTTP Data Collector API); Enterprise customers must migrate to the Cloudflare for Microsoft Sentinel Codeless Connector Framework (CCF) connector before that date.
Cloudflare Bot Management gains Adaptive Intelligence, a continuously self-rewriting detection engine that generates short-lived blocking rules in real time.
Adds Adaptive Intelligence to Cloudflare Bot Management: an ML detection engine that retrains continuously on live traffic, integrating new bot frameworks and bypass techniques in real time instead of waiting for scheduled updates. Adds multi-timeframe behavior analysis to catch low-and-slow attacks such as slow credential stuffing and scraping campaigns that evade traditional single-window detection. Combines browser-level session behavior signals from Cloudflare Precursor with global edge telemetry to evaluate automation and abuse beyond binary pass/fail tests. New security updates self-test against live traffic behind the scenes before deployment, verifying accuracy and avoiding false positives with zero downtime.
4 details in Everything
Load Balancing now supports pool sets
Aug 31, 2026
· release notes
Load Balancing now supports pool sets for location-specific traffic steering via the API.
Adds pool_sets field to the Load Balancing configuration to define location-specific routing rules Enables geographic matching (data center, country, region) within each pool set
2 details in Everything
Crawl endpoint now respects the Content Signals `use` directive
Aug 31, 2026
· release notes
Crawl endpoint now respects Content Signals use directive via new contentUse parameter
API surface changed: +230 endpoints, −142 endpoints, 271 modified, 22 deprecated
483 details in Everything
Cloudflare adds symmetric JWT JWT An open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object passed between parties. Cyber tools use it to verify identity and permissions without querying a central session store. GLM-5.3 Flash GLM-5.3 Flash A lightweight, fast large language model in Zhipu AI's GLM family, designed for low-latency inference, making it useful for cyber tools that need embedded AI reasoning without heavy compute overhead. multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats.
└──▷ USE IT
Stop a Durable Object alarm from retrying when the alarm's own cleanup work is complete, so the alarm handler does not re-run unnecessarily.
src/index.ts
copy
import { DurableObject } from 'cloudflare:workers';
export class CleanupTask extends DurableObject {
async alarm(): Promise<void> {
await this.ctx.storage.deleteAll();
this.ctx.abort('Cleanup complete', { retryAlarm: false });
}
}
Run the new multimodal GLM-5.3 Flash model on Workers AI for a text generation task with its large 1M-token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it.
javascript
copy
const response = await env.AI.run('@cf/zai-org/glm-5.3-flash', {
messages: [{ role: 'user', content: 'Summarize this incident report: ...' }]
});
Adds { retryAlarm: false } option to ctx.abort() on Durable Objects so interrupted alarms stop retrying instead of restarting after reset (requires Wrangler 4.126.0 or later for local dev). Adds deletion_protection field to Log Explorer dataset management: set it to false via the Update an account or zone dataset API method, then call the Delete an account or zone dataset method to permanently remove account or zone datasets. Symmetric HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it. HS256, HS384, HS512) are now supported for JWT validation, configurable via the Cloudflare dashboard or API. Durable Objects can now have up to ten concurrent Dynamic Workers with in-flight requests, up from four. Access service token Client Secrets created on or after August 26, 2026 use the scannable format cfast_[40 alphanumeric characters][8-character checksum], making them easier to detect with secret scanning secret scanning Checking files, code or other data for exposed credentials such as passwords, API keys and tokens. Findings help teams remove the secret and revoke or rotate it. CF-Access-Client-Id / CF-Access-Client-Secret headers are unchanged.
+6 more
show less
AI Search now supports six additional text generation models on Workers AI: @cf/deepseek-ai/deepseek-v4-flash-0731, @cf/deepseek-ai/deepseek-v4-pro-0813, @cf/openai/gpt-oss-120b, @cf/openai/gpt-oss-20b, @cf/qwen/qwen3.8-27b, and @cf/moonshotai/kimi-k2.7-code, with context windows context windows The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. AI Search now supports @cf/zai-org/glm-5.3-flash for text generation, with a 1,048,576-token context window. @cf/zai-org/glm-5.3-flash (GLM-5.3 Flash) is now available on Workers AI — the first natively multimodal GLM-5 model, with 320B total parameters (18B active per token on MoE MoE A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token. env.AI.run() , the REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. AI Search now supports larger custom metadata values within a shared 10 KiB metadata envelope per vector, with the first 64 UTF-8 bytes of each indexed string remaining filterable. Radar Researcher beta gains connected insights linking to Radar pages, reports, and blog posts, plus an Explain with AI button on URL Scanner reports for AI-driven findings explanations and follow-up Q&A. Cloudflare for Microsoft Sentinel Codeless Connector Framework (CCF) connector is now the supported replacement for the deprecated Azure Functions-based Microsoft Sentinel Logpush connector (end-of-life 2026-09-14).
11 details in Everything
└──▷ BREAKING ON UPGRADE
! Enterprise customers using the Azure Functions-based Microsoft Sentinel Logpush connector must migrate to the Cloudflare for Microsoft Sentinel CCF connector by 2026-09-14, when the underlying Microsoft Azure Monitor HTTP Data Collector API is retired and Cloudflare will stop maintaining the old connector.
Cloudflare adds Durable Objects concurrency bump, scannable Access token Access token A credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions.
New Access service token secrets now include a recognizable prefix and checksum, making them detectable by credential scanning tools. Log Explorer datasets (account and zone level) can now be permanently deleted from the Cloudflare dashboard or API. AI Search adds six new Workers AI models for text generation, plus GLM-5.3 Flash GLM-5.3 Flash A lightweight, fast large language model in Zhipu AI's GLM family, designed for low-latency inference, making it useful for cyber tools that need embedded AI reasoning without heavy compute overhead. Radar Researcher can now link to Radar pages, reports, and Cloudflare Blog posts, explain URL Scanner reports, and open shared sessions in fullscreen.
4 details in Everything
└──▷ BREAKING ON UPGRADE
! The Azure Functions-based Microsoft Sentinel Logpush Connector is deprecated; Cloudflare Enterprise customers must migrate to the Cloudflare for Microsoft Sentinel CCF connector by 2026-09-14.
Each Durable Object can now use up to ten Dynamic Workers with in-flight requests concurrently, raising the parallelism ceiling for stateful workloads.
└──▷ BREAKING ON UPGRADE
! Cloudflare Enterprise customers using the Azure Functions-based Microsoft Sentinel Logpush connector must migrate to the Cloudflare for Microsoft Sentinel CCF connector by 2026-09-14, after which the old connector will be deprecated.
Improved dataset configuration in Log Explorer
Aug 28, 2026
· release notes
Log Explorer introduces grouped field selection, bulk controls, and ingestion filters for dataset configuration
Grouped field selection organizes fields by category and shows the number selected in each group within Log Explorer datasets.Field details displays data type information and marks required or deprecated fields for Log Explorer datasets.Bulk controls allow selecting all fields or resetting selection to dataset defaults in Log Explorer.Ingestion filters enable ingesting all events or filtering by specific conditions in Log Explorer datasets.
4 details in Everything
Durable Objects can use up to ten Dynamic Workers concurrently
Aug 28, 2026
· release notes
Durable Objects can use up to ten Dynamic Workers concurrently (up from four)
Cloudflare One Client for Windows (version 2026.7.1376.0)
Aug 28, 2026
· release notes
Cloudflare One Client for Windows reaches general availability.
Z.ai GLM-5.3 now available on Workers AI
Aug 28, 2026
· release notes
Z.ai GLM-5.3 model added to Workers AI with @cf/zai-org/glm-5.3 identifier
Adds @cf/zai-org/glm-5.3, Z.ai's flagship agentic coding model, to Workers AI for long-running tool-driven workflows Enables invocation of GLM-5.3 via the OpenAI-compatible endpoint on Workers AI
2 details in Everything
API Shield - Increased limits for JWT validation configurations (2026-08-27)
Aug 27, 2026
· release notes
API Shield JWT JWT An open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object passed between parties. Cyber tools use it to verify identity and permissions without querying a central session store.
Increases the default number of JSON Web Token configurations allowed per zone from previous limit to 32
1 detail in Everything
Cloudflare AI adds Wan 3.0 text-to-video, AssemblyAI Universal-3.5 Pro transcription, FLUX Kontext image models, and FLUX Video Upscale
Adds wan-3.0, Alibaba's text-to-video model, supporting adaptive aspect ratio and 480P, 720P, or 1080P resolution output with configurable duration. Adds universal-3.5-pro, AssemblyAI's Universal-3.5 Pro speech recognition model for fast, high-accuracy transcription. Adds flux-1-kontext-max, Black Forest Labs' highest-quality Kontext model for text-to-image generation and context-aware image editing. Adds flux-1-kontext-pro for text-prompted image creation and editing with strong character and style consistency. Adds flux-video-upscale (video-to-video), a FLUX Video Upscale model with a precise mode for source-faithful results and a creative mode for stronger detail enhancement, accepting clips up to 20 seconds with audio preserved.
5 details in Everything
Cloudflare adds app-scoped API tokens, Access token Access token A credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions. CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic. DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest. WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ TRY IT
Fetch a live ASPA snapshot from Cloudflare Radar to power your own BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
copy
$ curl https://api.cloudflare.com/client/v4/radar/bgp/rpki/aspa/snapshot Set up a CASB remediation policy that auto-revokes external Google Workspace file shares and notifies a webhook the moment a finding is detected.
📍 In Cloudflare One, go to Cloud & SaaS findings › Policies › Create a policy. Under Basic information enter a Policy name. Under Choose how you want to trigger the policy select Vendor: Google, Integration: Google Workspace, and the desired Finding type. Under Define what to do with findings that match your trigger enable both Run Remediation and Send webhooks. Under Status enable Enable policy, then select Create policy.
Adds Specified Flagship apps resource scope when creating custom API tokens, with Flagship App permission levels of Evaluate, Read, or Write — limiting token access to selected apps instead of the entire account. Cloudflare Access now lets administrators choose a grace period (1 hour to 30 days) when rotating a service token secret, keeping both secrets valid during rotation; the API accepts an RFC 3339 expiration time for custom schedules. Cloudflare Access administrators can now temporarily disable service tokens without deleting them, halting authentication (including any active rotation grace period) while preserving configuration for later re-enablement. MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. /mcp endpoint now accepts stateless MCP 2026-07-28 requests alongside earlier 2025 Streamable HTTP Streamable HTTP An MCP transport protocol that lets a client send JSON-RPC requests over HTTP POST while the server streams responses back using Server-Sent Events, replacing the older stdio and SSE transports for remote tool communication. SSE SSE Server-Sent Events, a browser API and HTTP-based protocol where a server pushes a stream of text events to a client over a single long-lived connection, giving tools a lightweight alternative to WebSockets for one-way real-time updates. WAF moves HTTP/2 Request Smuggling - Request Body Anomaly and XSS XSS Cross-site scripting, an attack that runs malicious script in another user's browser through a trusted site. It can steal data or perform actions using the user's session.
+7 more
show less
Cloudflare One Virtual Appliance dashboard now lets administrators select a hypervisor (VMware ESXi, Proxmox, libvirt/KVM KVM A Linux kernel module that turns the kernel into a hypervisor, letting a process run fully isolated virtual machines using hardware virtualisation extensions. Cyber tools use it to sandbox execution environments at near-native speed. OVA OVA An Open Virtualization Appliance file — a single portable package containing a virtual machine disk image and its configuration metadata, standardized by the DMTF, letting cyber tools ship as ready-to-run VM bundles. Cloudflare Radar adds an ASPA validation tool in the Routing section: enter a BGP AS_PATH and check it against live RPKI ASPA records per draft-ietf-sidrops-aspa-verification, returning Valid/Invalid/Unknown verdicts for both Upstream (section 5.4) and Downstream (section 5.5) algorithms; path and algorithm are preserved in the URL for sharing. The /bgp/rpki/aspa/snapshot Cloudflare Radar API endpoint supplies the ASPA record snapshot used by the validation tool. Wrangler (wrangler login) and the Cloudflare API MCP server now present an OAuth consent dialog that lets users select individual optional scopes rather than approving all scopes; declining a scope and then needing it requires reauthorization. Cloudflare CASB now supports remediation policies that automatically revoke external sharing on Microsoft 365 and Google Workspace file-sharing findings, and/or send posture finding data to Slack, ServiceNow, or any webhook destination, without manual triage. Cloudflare DLP adds a Test scan capability: paste text, upload a file, or upload a HAR HAR An HTTP Archive file, a JSON-format log of all network requests and responses captured by a browser's developer tools, used by cyber tools to replay, inspect, or analyze web traffic without re-running a live session. OCR OCR Optical character recognition, converting text in an image or scanned document into machine-readable characters. It lets software search or process text that was stored as pixels. Cloudflare API 403 Forbidden responses now include a documentation_url field pointing directly to the API documentation for the denied endpoint.
12 details in Everything
Cloudflare API adds email security content policies, logpush transformers, AI Security for Apps, leaked credential checks, and content scanning endpoints
└──▷ TRY IT
Bulk-import email sending suppressions in one call to avoid sending to known-bad addresses across your account.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/{account_id}/email/sending/suppressions/bulk' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' \
-d '{"suppressions": [{"email": "bounce@example.com", "reason": "hard_bounce"}, {"email": "spam@example.com", "reason": "spam_complaint"}]}' Preview a new Logpush transformer to validate its output before saving it to a pipeline.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/{account_id}/logpush/transformers/preview' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' \
-d '{"expression": "...", "sample": {}}'
Adds full CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. /accounts/{account_id}/email-security/settings/content_policies (list, get, create, update, delete, and batch operations). Adds full CRUD API for account email sending suppressions via /accounts/{account_id}/email/sending/suppressions, including bulk import at /accounts/{account_id}/email/sending/suppressions/bulk. Adds full CRUD API for Logpush transformers via /accounts/{account_id}/logpush/transformers, with additional endpoints to preview (/preview), retrieve content (/{transformer_id}/content), and list versions (/{transformer_id}/versions). Adds API endpoints for API discovery operation labels: list, create, delete, get, update, edit, and delete user-defined labels, plus managed label read and replace endpoints. Adds endpoints to export discovered API operations as OpenAPI OpenAPI A vendor-neutral specification for describing REST APIs in a machine-readable format, maintained by the OpenAPI Initiative. Cyber tools use it to auto-generate clients, documentation, and validation from a single source of truth.
+12 more
show less
Adds token validation configuration endpoints: get, create, edit, and delete a token validation configuration, replace/edit token validation credentials, and create/edit/get/delete token validation rules. Adds Get NEL setting and Edit NEL setting endpoints at /zones/{zone_id}/settings/nel. Adds endpoints to get and update session identifier settings. Adds endpoints to get and update client-side security settings, and to list/get/create/update/delete content security rules. Adds endpoints to list and get detected connections, scripts, and cookies for client-side security. Adds leaked credential check endpoints: get/update zone status, and list/create/get/update/delete custom detection locations. Adds content scanning endpoints: enable, disable, get/update status, list/create/delete custom expressions for a zone. Adds Get AI Security for Apps status and Update AI Security for Apps status endpoints, plus get/update custom topics for a zone. Adds credential set and credential management endpoints (list, create, get, update, edit, delete) along with scan and target environment CRUD endpoints. Adds a Generate a fallthrough WAF expression template endpoint. Adds Get Tunnel configuration and Update Tunnel configuration endpoints. Bumps the Cloudflare Go SDK to v7.9.0 (install via go get -u github.com/cloudflare/cloudflare-go/v7@v7.9.0) and API spec to version 5.24.0.
17 details in Everything
Cloudflare adds app-scoped API tokens, service token grace periods, RPKI ASPA path validation, and virtual appliance downloads from the dashboard.
└──▷ HOW TO FIND IT
Validate a BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
📍 In Cloudflare Radar, navigate to the RPKI ASPA path validation tool, enter the BGP AS path you want to verify, and review the verdict, provider authorizations, and step-by-step verification trace.
Download the Cloudflare One Virtual Appliance to deploy a connector in your on-premises hypervisor environment without hunting for an external download link.
📍 In the Cloudflare dashboard, go to Cloudflare One › Connectors, select your hypervisor type, then download the virtual appliance image or install script.
Adds app-scoped API tokens for Flagship, allowing a Cloudflare API token to be scoped to selected Flagship apps instead of every app in the account. Adds grace periods for service token rotation, keeping the previous service token secret active while its replacement is deployed. Adds the ability to temporarily disable an Access service token to stop it from authenticating without deleting its configuration. MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Adds RPKI ASPA path validation on Cloudflare Radar — validates any BGP AS path against published RPKI ASPA records, returning a verdict, provider authorizations, and a step-by-step trace of the verification algorithm.
+1 more
show less
Cloudflare One Virtual Appliance images and install scripts can now be downloaded directly from the Connectors page in the dashboard by selecting the target hypervisor.
6 details in Everything
Cloudflare adds app-scoped API tokens, service token grace periods/toggles, RPKI ASPA path validation on Radar, and MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
└──▷ HOW TO FIND IT
Validate a BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
📍 In Cloudflare Radar, navigate to the RPKI ASPA path validation tool, enter the BGP AS path to inspect, and review the verdict, provider authorizations, and step-by-step verification trace.
Download the Cloudflare One Virtual Appliance for your environment without leaving the dashboard.
📍 In the Cloudflare dashboard, go to Cloudflare One › Connectors, select your hypervisor, and download the virtual appliance image or install script.
Create app-scoped API tokens for Flagship
Aug 26, 2026
· release notes
Cloudflare Flagship adds app-scoped API tokens limiting access to specified apps
Introduces granular Flagship App permissions (Evaluate, Read, Write) for app-scoped tokens, restricting access to specific functions on selected apps.
1 detail in Everything
Radar Researcher adds richer sources and URL Scanner explanations
Aug 26, 2026
· release notes
Radar Researcher beta expands with richer data sources and URL Scanner explanations
Adds linked Radar pages, reports, and Blog posts within Radar Researcher responses for connected insights. Enables Explain with AI action on URL Scanner reports to generate AI explanations and answer follow-up questions. Improves shared session experience by opening conversations in fullscreen mode.
3 details in Everything
Cloudflare Log Explorer adds API and UI capability to permanently delete account and zone datasets.
Adds the ability to permanently delete Log Explorer datasets via the API using deletion_protection flag and dedicated deletion endpoints. Adds Manage datasets UI workflow with Delete action and name confirmation in Cloudflare dashboard.
2 details in Everything
New Workers AI text generation models in AI Search
Aug 26, 2026
· release notes
AI Search adds Workers AI text generation models (DeepSeek, GPT OSS OSS Open-source software: code whose licence permits anyone to inspect, modify, and redistribute it. Cyber tools build on it to reuse auditable libraries without licensing fees.
Enables selection of these new text generation models when creating or updating an AI Search instance via the dashboard or API without requiring a provider key.
1 detail in Everything
WAF Release - 2026-08-26 - Emergency
Aug 26, 2026
· release notes
Emergency WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives.
Z.ai GLM-5.3 Flash now available on Workers AI
Aug 26, 2026
· release notes
Z.ai GLM-5.3 Flash GLM-5.3 Flash A lightweight, fast large language model in Zhipu AI's GLM family, designed for low-latency inference, making it useful for cyber tools that need embedded AI reasoning without heavy compute overhead. multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats.
Adds support for the @cf/zai-org/glm-5.3-flash model in Workers AI, enabling multimodal inputs via the REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
1 detail in Everything
API Shield - Symmetric key support for JWT validation (2026-08-25)
Aug 25, 2026
·
issue 058
API Shield JWT JWT An open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object passed between parties. Cyber tools use it to verify identity and permissions without querying a central session store. HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it.
HMAC verification keys can be configured via the Cloudflare dashboard or the Cloudflare API; credentials are never stored in plaintext and are never returned in API responses.
1 detail in Everything
WAF - WAF Release - 2026-08-25 (2026-08-25)
Aug 25, 2026
·
issue 057
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Promotes HTTP/2 Request Smuggling - Request Body Anomaly (rule ...1489d892) from Log to Block in the Cloudflare Managed Ruleset. Promotes XSS - JavaScript Event Handler Coercion - Headers (rule ...20646260) from Log to Block in the Cloudflare Managed Ruleset. Promotes XSS - JavaScript Event Handler Coercion - Body (rule ...d706d517) from Log to Block in the Cloudflare Managed Ruleset. Promotes XSS - JavaScript Event Handler Coercion - URI (rule ...660886c8) from Log to Block in the Cloudflare Managed Ruleset. Adds Generic Rules - Remote Code Execution (rule ...2ca6cce3) as a new detection in Block mode to the Cloudflare Managed Ruleset.
+1 more
show less
Merges XSS, HTML Injection - Script Tag - Beta (rule ...c293b926) into the original XSS, HTML Injection - Script Tag rule (...7b58420b).
6 details in Everything
└──▷ BREAKING ON UPGRADE
! Rules ...1489d892, ...20646260, ...d706d517, and ...660886c8 change from Log to Block — traffic previously only logged for HTTP/2 Request Smuggling and XSS XSS Cross-site scripting, an attack that runs malicious script in another user's browser through a trusted site. It can steal data or perform actions using the user's session. ! Rule ...c293b926 (XSS, HTML Injection - Script Tag - Beta ) is merged into ...7b58420b; any overrides or exceptions referencing the Beta rule ID will no longer apply.
Prevent Durable Object alarm retries when using `ctx.abort()`
Aug 25, 2026
· release notes
Adds retryAlarm:false option to ctx.abort() to prevent Durable Object alarm retries.
Adds retryAlarm configuration option to the second argument of ctx.abort() to control alarm retry behavior.
1 detail in Everything
MCP server portals support MCP 2026-07-28 specification
Aug 25, 2026
· release notes
Cloudflare MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. /mcp.
/mcp endpoint automatically accepts stateless MCP 2026-07-28 requests and earlier 2025 Streamable HTTP Streamable HTTP An MCP transport protocol that lets a client send JSON-RPC requests over HTTP POST while the server streams responses back using Server-Sent Events, replacing the older stdio and SSE transports for remote tool communication. Upstream connections check for MCP 2026-07-28 support and fall back to the 2025 handshake when needed
2 details in Everything
Temporarily turn off Access service tokens
Aug 25, 2026
· release notes
Cloudflare Access adds ability to temporarily disable service tokens without deletion.
Adds the ability for administrators to temporarily turn off Access service tokens, allowing configuration to remain while stopping authentication New control stops previous secrets in an active rotation grace period when a token is disabled
2 details in Everything
RPKI ASPA path validation on Cloudflare Radar
Aug 24, 2026
· release notes
Cloudflare Radar adds an ASPA validation tool to the Routing section for checking BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes. AS_PATHs against RPKI records.
Adds an ASPA validation tool in the Radar Routing section that accepts a BGP AS_PATH, loads the full RPKI ASPA snapshot, and returns a verdict of Valid , Invalid , or Unknown against the draft-ietf-sidrops-aspa-verification standard. Supports verifying paths using both Upstream (section 5.4) and Downstream (section 5.5) algorithms simultaneously, labeling each with its respective verdict to detect route leaks based on whether a down-ramp is permitted. Displays an ASPA validation graph that highlights hops as Provider+ , Not Provider+ , or No attestation , and includes an Algorithm step by step section showing the derivation of the verdict under upper bounds (Invalid) and lower bounds (Unknown) stopping rules.
3 details in Everything
Preserve exception details in console logs
Aug 24, 2026
· release notes
Workers now preserve exception name, message, and stack in console logs, with errorInfo array for Tail Workers.
Console methods now include the exception name, message, and stack trace when logging an error via console.error() Tail Workers receive a new errorInfo array in log entries that maps structured error details to corresponding message arguments
2 details in Everything
Cloudflare adds CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic.
└──▷ TRY IT
Inspect a Cloudflare API 403 response to immediately identify which docs page lists the required roles for the denied endpoint.
copy
$ curl -s -o response.json -w "%{http_code}" -X GET \
"https://api.cloudflare.com/client/v4/workers/scripts" \
-H "Authorization: Bearer <token>" && \
cat response.json | jq '.errors[0].documentation_url' Create a CASB remediation policy that auto-revokes external sharing on Google Workspace file-sharing findings and sends a webhook to Slack.
📍 In Cloudflare One, go to Cloud & SaaS findings › Policies, select Create a policy , enter a Policy name, set Vendor to Google Workspace and the relevant Integration and Finding type, then under 'Define what to do with findings that match your trigger' enable both Run Remediation and Send webhooks , then toggle Enable policy and select Create policy .
Cloudflare API 403 Forbidden responses now include a documentation_url field pointing directly to the denied endpoint's API documentation, surfacing required roles for faster self-service troubleshooting and enabling agents to drive approval workflows from error context. Adds CASB remediation policies in Cloudflare One to automatically remediate file-sharing findings in Microsoft 365 and Google Workspace — or send webhooks to Slack, ServiceNow, or any destination — the moment CASB detects a finding, with no manual triage. OAuth clients can now classify configured scopes as required or optional in the Cloudflare dashboard; users see Read Only and Full Access templates and a scope search on the consent screen, and can decline optional scopes to enforce least-privilege access. wrangler login now presents an Edit optional permissions step during authorization, letting users choose which optional OAuth scopes to grant Wrangler or the Cloudflare API MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Browser Rendering (Workers Paid plan) default limits raised: concurrent browsers 120 → 200, new browser instances/second 1 → 3, Quick Actions requests/second 10 → 30.
+3 more
show less
Miniflare now automatically grants FUSE FUSE A Linux kernel interface that lets userspace programs implement a filesystem without kernel code, maintained as part of the kernel project; tools use it to mount virtual or synthetic filesystems without requiring root or kernel modules. WSL WSL Windows Subsystem for Linux, a Microsoft-built compatibility layer that lets a Linux environment run directly on Windows without a virtual machine, giving cyber tools access to Linux binaries, filesystems, and syscalls on a Windows host. /dev/fuse is available, enabling use cases such as mounting R2 buckets with FUSE. Durable Object namespaces gain a Deployments tab in the Cloudflare dashboard showing live Worker versions, traffic split, requests, error rate, and wall time per version — including actual observed traffic share alongside the configured percentage. Web Analytics extends navigationType values to navigate, soft-navigation (Chrome Soft Navigation API), and routing-apis (Navigation API / History API fallback), adding native LCP LCP Link Control Protocol, part of PPP, negotiates and configures point-to-point data links between two peers. Cyber tools targeting PPP-based connections use it to inspect or manipulate link establishment.
8 details in Everything
└──▷ BREAKING ON UPGRADE
! Web Analytics may report a different volume of pageviews after the soft navigation measurement update — the extent depends on front-end architecture and visitor traffic patterns.
Choose OAuth scopes for Wrangler and the Cloudflare API MCP server
Aug 22, 2026
· release notes
Wrangler and Cloudflare API MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds the ability to edit and select optional OAuth scopes for Wrangler and the Cloudflare API MCP server during the consent dialog. Required OAuth scopes remain selected by default while optional scopes are now user-selectable.
2 details in Everything
Saved login profiles for returning users
Aug 21, 2026
· release notes
Cloudflare Dashboard now supports saving login profiles on-device for returning users
Adds ability to save up to five login profiles (email, method, last-used) per device in the Cloudflare Dashboard
1 detail in Everything
Test Data Loss Prevention profiles without sending traffic through Gateway
Aug 21, 2026
· release notes
Adds Test scan UI to evaluate DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Adds a Test scan interface in the Cloudflare Zero Trust console allowing users to paste text, upload files, or upload HAR HAR An HTTP Archive file, a JSON-format log of all network requests and responses captured by a browser's developer tools, used by cyber tools to replay, inspect, or analyze web traffic without re-running a live session.
1 detail in Everything
Web Analytics improves soft navigation measurement for Single Page Applications (SPAs)
Aug 21, 2026
· release notes
Cloudflare Web Analytics adds soft-navigation and routing-apis navigation types to accurately measure SPAs.
Adds soft-navigation value to navigationType for native Soft Navigation API measurements Adds routing-apis value to navigationType for fallback soft navigation detection via Navigation/History APIs
2 details in Everything
Automatically remediate Microsoft 365 and Google Workspace findings with API-based CASB remediation policies
Aug 21, 2026
· release notes
New CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic.
Adds CASB remediation policies to automatically fix SaaS SaaS Software delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally. Supports first-party remediation actions against the Microsoft 365 integration API for file-sharing findings Supports sending posture finding data to Slack, ServiceNow, or any webhook destination via policy actions
3 details in Everything
Enriched 403 responses for the Cloudflare API
Aug 21, 2026
· release notes
Cloudflare API now includes documentation_url in enriched 403 responses to link directly to endpoint docs
Adds documentation_url field to 403 error responses across nearly all Cloudflare product APIs
1 detail in Everything
Cloudflare Wallets introduces programmable Account and Virtual Wallets for AI agents, with handle reservation now live at cloudflare.pay.
Introduces Cloudflare Wallets, a programmable wallet system giving Cloudflare accounts and AI agents a stable identity and a mechanism to pay for APIs and content using stablecoins. Introduces Account Wallets for human account owners, supporting fund management, spend delegation to agent-controlled Virtual Wallets, and a stable cloudflare.pay identifier. Introduces Virtual Wallets for AI agents, operated via API keys, with spend permissions and a maximum spend cap set by the Account Wallet owner — enabling autonomous agent spending without per-action manual approval. Wallet handles can be reserved now at cloudflare.pay (one per Cloudflare account), publishing a page at HANDLE.cloudflare.pay and registering the account for early access when full wallet functionality launches. Integrates with Agentic Payments to enable agents to charge for or pay for HTTP content and MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. x402 x402 A proposed HTTP payment protocol revival using status code 402, enabling machine-to-machine micropayments over HTTP so cyber tools can gate API access or resources behind automated, per-request cryptocurrency payments.
5 details in Everything
Cloudflare AI Models catalog adds nine new models spanning image generation, video, and agentic LLMs LLMs A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code.
Adds qwen-image-3.0-pro (Alibaba): text-to-image model supporting up to 6 image variants per call, negative prompts, seed control, and optional prompt rewriting, with strengths in complex layout generation, small-text precision, and multilingual font rendering. Adds qwen3.7-max (Alibaba): flagship agent-centric LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code. Adds qwen3.7-plus (Alibaba): cost-effective Qwen3.7 model with image and video understanding plus full-stack agent intelligence for coding, tool use tool use A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions. GUI GUI A graphical user interface, controls such as windows, buttons and menus. It lets people use software visually rather than entering commands. Adds qwen3.8-max (Alibaba): 2.4-trillion-parameter MoE MoE A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token. Adds Claude Opus 5 (Anthropic): complex agentic coding and enterprise model with adaptive thinking, one million token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it.
+4 more
show less
Adds ByteDance's next-generation video model: unified multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. Adds gemini-3.7-flash (Google): natively multimodal reasoning model optimized for agentic workflows and real-world tasks. Adds ltx-2-5-fast (Lightricks): fast video generation model for text-to-video and image-to-video workflows with synchronized audio, configurable duration, resolution, and frame rate. Adds grok-imagine-image-2.0 (xAI): image generation and editing model with strong instruction following, typography, layout, and reference-image preservation.
9 details in Everything
Cloudflare adds HTTP Basic Auth leaked-credential scanning, R2 us jurisdiction, post-quantum post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA. SMTP SMTP The application-layer protocol used to send email between servers and from clients to servers; cyber tools use it to relay alerts, phishing simulations, or exfiltrated data over standard mail infrastructure.
└──▷ USE IT
Create an R2 bucket with US data residency from a Workers configuration to meet explicit US data-locality requirements.
wrangler.toml
copy
[[r2_buckets]]
binding = "MY_BUCKET"
bucket_name = "<YOUR_BUCKET_NAME>"
jurisdiction = "us"
R2 now supports a us jurisdiction guaranteeing data is stored and processed within the United States; access buckets via the jurisdiction-specific S3 endpoint https://<ACCOUNT_ID>.us.r2.cloudflarestorage.com or set jurisdiction = "us" in a [[r2_buckets]] Workers binding. Cloudflare Email Security now negotiates X25519MLKEM768 post-quantum hybrid key exchange on inbound MX and outbound SMTP delivery connections when the peer supports it, protecting mail traffic against harvest-now, decrypt-later attacks; backwards compatible and enabled automatically for all Email Security packages. AI Gateway adds support for the openai/gpt-5.6-sol model at 50% promotional pricing ($2.50/1M input tokens, $15/1M output tokens, $0.25/1M cache-read tokens) through September 18, 2026 for non-BYOK BYOK Bring Your Own Key — a cloud deployment model where the customer supplies and controls the encryption keys rather than the provider, so sensitive data stays under the customer's cryptographic authority. Load balancing analytics pool filter now queries by pool name instead of internal pool ID, fixing filtering for the Requests over time , Pool distribution , Top endpoints , and Latency views. Cloudflare One Client (Windows, macOS, Linux) version 2026.7.1343.0 graduates to stable: clearer reauthentication notifications with browser redirect, and adaptive HTTP/3 HTTP/3 The third major version of HTTP, standardized by the IETF, which runs over QUIC instead of TCP, eliminating head-of-line blocking and reducing connection latency for faster, more resilient data transfer.
5 details in Everything
Cloudflare Wallets lets accounts and agents reserve a stable, human-readable wallet handle for agentic payments.
Leaked credentials detection gains Authorization header scanning, Tunnel gets dashboard origin config, and Email Security adds post-quantum key exchange post-quantum key exchange A cryptographic handshake algorithm designed to resist attacks from quantum computers, using math problems like lattices that quantum algorithms cannot efficiently solve, letting tools stay secure against future quantum-capable adversaries.
Cloudflare Tunnel now supports configuring origin application parameters — including TLS verification, HTTP Host header, and connection timeouts — directly in the Cloudflare dashboard when editing a published application. Cloudflare Email Security adds post-quantum post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA. SMTP SMTP The application-layer protocol used to send email between servers and from clients to servers; cyber tools use it to relay alerts, phishing simulations, or exfiltrated data over standard mail infrastructure. Load balancing analytics pool filter now queries by pool name instead of pool ID, aligning filter behavior with the UI dropdown display. Cloudflare One Client version 2026.7.1343.0 released for Windows, macOS, and Linux.
4 details in Everything
Cloudflare adds Basic Auth leaked credential scanning, post-quantum post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA. SMTP SMTP The application-layer protocol used to send email between servers and from clients to servers; cyber tools use it to relay alerts, phishing simulations, or exfiltrated data over standard mail infrastructure.
Cloudflare Tunnel now supports configuring origin parameters — including TLS verification, HTTP Host header, and connection timeouts — directly in the Cloudflare dashboard when editing a published application. Cloudflare Email Security supports post-quantum hybrid key exchange on inbound and outbound SMTP connections for MX deployments. Load balancing analytics pool filter now queries by pool name instead of pool ID, aligning the filter with the UI dropdown display. Cloudflare One Client version 2026.7.1343.0 released for Windows, macOS, and Linux.
4 details in Everything
WAF - Leaked credentials detection now scans Authorization headers (2026-08-20)
Aug 20, 2026
·
issue 051
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Matches populate existing fields such as cf.waf.credential_check.password_leaked and trigger the Exposed-Credential-Check managed transform header when configured, so existing custom rules and rate limiting rules apply without modification.
1 detail in Everything
Run more headless browsers concurrently with Browser Run
Aug 20, 2026
· release notes
Browser Run raises default concurrency limits on Workers Paid plan
Concurrent browsers limit increased from 120 to 200 for Workers Paid plansNew browser instances / second rate limit increased from 1 to 3 for Workers Paid plansQuick Actions requests / second limit increased from 10 to 30 for Workers Paid plans
3 details in Everything
Per-zone post-quantum visibility in Logpush and Log Explorer
Aug 20, 2026
· release notes
Adds ClientTLSKeyExchangeGroup field to Logpush and Log Explorer for per-zone PQ traffic visibility
Introduces the ClientTLSKeyExchangeGroup field in the http_requests Logpush dataset and Log Explorer to identify TLS key exchange groups (e.g., X25519MLKEM768, X25519X25519 The elliptic-curve key exchange most modern TLS, SSH and WireGuard connections use to agree on a session key. Post-quantum hybrids pair it with ML-KEM. Enables building per-zone reports of post-quantum post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA.
2 details in Everything
Cloudflare GA introduces optional OAuth scopes and new consent screen templates.
Adds the ability to classify configured OAuth client scopes as optional in the Cloudflare dashboard Introduces Read Only and Full Access scope selection templates on the consent screen Enables users to search for specific scopes directly within the consent screen interface
3 details in Everything
View deployments for Durable Objects in the dashboard
Aug 20, 2026
· release notes
New Deployments tab in Cloudflare dashboard for Durable Object namespaces showing live versions and actual traffic splits.
Adds a Deployments tab to Durable Object namespaces in the Cloudflare dashboard to show live Worker versions and observed traffic split alongside metrics like requests, error rate, and wall time. Updates the Traffic % column in both Workers and Durable Objects deployments to display the actual, observed traffic share for each version next to the configured percentage.
2 details in Everything
Use FUSE in local Containers development
Aug 20, 2026
· release notes
Miniflare now grants FUSE FUSE A Linux kernel interface that lets userspace programs implement a filesystem without kernel code, maintained as part of the kernel project; tools use it to mount virtual or synthetic filesystems without requiring root or kernel modules.
New Logpush datasets and updated fields across multiple Logpush datasets in Cloudflare Logs
Aug 20, 2026
· release notes
New Logpush datasets for Account Abuse Protection Events and Magic BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
Adds Account Abuse Protection Events dataset to Logpush with fields like AuthenticationIdentityProvider, BotScore, ClientIP, FraudEmailRisk, and UserID. Adds Magic BGP Logs dataset to Logpush with fields including Direction , EventKind, TunnelID, and TunnelName. Adds AISecurityCustomTopicCategories, WAFRequestSignatureCategories, and WAFRequestSignatureRefs fields to existing Firewall events , HTTP requests , and other Logpush datasets.
3 details in Everything
Cloudflare One Client for Linux (version 2026.7.1343.0)
Aug 19, 2026
· release notes
Cloudflare One Client for Linux 2026.7.1343.0 adds browser-based reauthentication and adaptive HTTP/2-first fallback for restricted networks.
Introduces clearer reauthentication notifications that redirect to the browser when necessary, reducing steps to regain access after session expiry. Adds adaptive network learning that prioritizes HTTP/2 over HTTP/3 HTTP/3 The third major version of HTTP, standardized by the IETF, which runs over QUIC instead of TCP, eliminating head-of-line blocking and reducing connection latency for faster, more resilient data transfer.
2 details in Everything
Cloudflare One Client for Windows (version 2026.7.1343.0)
Aug 19, 2026
· release notes
The Windows Cloudflare One Client reaches GA with improved HTTP/2 fallback logic and browser-based reauthentication flows.
Threat Intel Lists supported in Unified Routing
Aug 19, 2026
· release notes
Threat Intel Lists now supported in Unified Routing mode.
Cloudflare One Client for macOS (version 2026.7.1343.0)
Aug 19, 2026
· release notes
Cloudflare One Client for macOS GA release with adaptive HTTP fallback and improved reauth UX
Adds adaptive network learning to prioritize HTTP/2 over HTTP/3 HTTP/3 The third major version of HTTP, standardized by the IETF, which runs over QUIC instead of TCP, eliminating head-of-line blocking and reducing connection latency for faster, more resilient data transfer. Improves reauthentication flow by redirecting users to the browser instead of the app window when necessary.
2 details in Everything
Access resource lists now support resource-scoped roles
Aug 19, 2026
· release notes
Cloudflare Access resource lists now support resource-scoped roles in the dashboard and API
Members with only resource-scoped Access roles can now open Access resource list pages in the Cloudflare dashboard API list endpoints return resources filtered to the member's permission policy scopes, removing the need for account-scoped read-only roles
2 details in Everything
Cloudflare Workers AI adds four new models: Grok 4.6, DeepSeek-V4-Flash-0731, DeepSeek V4 Pro, and Qwen 3.8 27B.
Adds grok-4.6 (xAI Grok 4.6) to Workers AI — a flagship reasoning model supporting text and image inputs, function calling function calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions. structured outputs structured outputs Forcing a model's response to match a given format or JSON schema, so software can parse it reliably instead of hoping the text is well formed. Adds deepseek-v4-flash-0731 (DeepSeek-V4-Flash official release) to Workers AI, superseding the preview version with substantially enhanced agentic capabilities. Adds deepseek-v4-pro-0813 (DeepSeek V4 Pro) to Workers AI — a high-capability reasoning model with a one-million-token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. Adds qwen3.8-27b (Qwen 3.8 27B, Image-Text-to-Text) to Workers AI — a 27-billion-parameter instruction-tuned model from Alibaba supporting vision, general-purpose text generation, and agentic workloads.
4 details in Everything
Cloudflare adds package registry security with pkg.* selectors, Qwen/DeepSeek models on Workers AI, Worker-level Access policies, and CT Monitoring GA
└──▷ HOW TO FIND IT
Block downloads of a specific npm package from any registry (including corporate proxies) in a Gateway HTTP policy.
📍 # In Zero Trust dashboard: Settings › Gateway › HTTP Policies › Add a rule
# Selector: Package Ecosystem = npm
# Then add nested selector: pkg.name = lodash
# Action: Block
# Or via API — the selectors to reference are pkg.ecosystem and pkg.name
Create an Artifacts namespace pinned to the EU for GDPR GDPR EU regulation enacted in 2018 that governs how organizations collect, store, and process personal data of EU residents, giving cyber tools legal obligations around data handling and breach notification.
copy
$ curl --request POST \
--url "https://api.cloudflare.com/client/v4/accounts/$ACCOUNT_ID/artifacts/namespaces" \
--header "Authorization: Bearer $CLOUDFLARE_API_TOKEN" \
--header "Content-Type: application/json" \
--data '{"namespace": "my-eu-namespace", "jurisdiction": "eu"}' Test an Access-protected Worker locally using a mock identity without deploying.
wrangler.jsonc
copy
{
"access": {
"dev": {
"aud": "my-app",
"identity": {
"email": "admin@example.com"
}
}
}
}
Adds pkg.ecosystem, pkg.name, pkg.version, pkg.namespace, and pkg.purl selectors to Cloudflare Gateway HTTP policies so teams can allow or block software package downloads by ecosystem (npm, PyPI, RubyGems, Cargo, Go, Maven, NuGet NuGet Microsoft's package manager for .NET, hosting a public registry of reusable libraries so tools can pull in dependencies without bundling or manually maintaining third-party code. PURL PURL A Package URL — a community-maintained spec for identifying software packages across ecosystems (npm, PyPI, Maven, etc.) with a single, consistent string, letting cyber tools pinpoint exact dependencies unambiguously. pkg.purl is API-only. Requires TLS decryption. Adds ctx.access.getIdentity() on the ctx.access object inside Workers so authenticated requests expose the user's email, name, and groups without manual JWT JWT An open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object passed between parties. Cyber tools use it to verify identity and permissions without querying a central session store. Adds an access.dev block to wrangler.jsonc for locally simulating Cloudflare Access — set aud and a mock identity (e.g., email) to test authenticated and unauthenticated flows without deploying. Adds jurisdiction field to the Artifacts namespace creation API (POST /client/v4/accounts/{account_id}/artifacts/namespaces) supporting 'eu' and 'us' values for data localization; jurisdiction is immutable after namespace creation. Adds @cf/qwen/qwen3.8-27b to Workers AI — a 27B-parameter vision language model with a 262,144-token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. function calling function calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions. POST /ai/run.
+4 more
show less
Adds @cf/deepseek-ai/deepseek-v4-pro-0813 and @cf/deepseek-ai/deepseek-v4-flash-0731 to Workers AI with a 1,048,576-token context window, thinking mode, and function calling; available via Workers AI binding, REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Enables attaching a Cloudflare Access policy to a Worker directly so all associated domains, routes, and preview URLs are protected automatically — including a 'protect all Workers by default' option with per-Worker bypass. Adds ordered, maxRetransmits, and maxPacketLifeTime fields to the Realtime SFU SFU A Selective Forwarding Unit: a media server architecture that relays incoming WebRTC streams to other participants without decoding them, reducing server CPU cost and latency in multi-party video or data pipelines. POST /v1/apps/{app_id}/sessions/{session_id}/datachannels/new) enabling unordered and partially reliable delivery modes. Certificate Transparency Certificate Transparency A public, append-only log system maintained by various operators (Google runs several) that records every TLS certificate issued, letting anyone audit CAs for misissued or rogue certificates.
9 details in Everything
Cloudflare API adds Image Transformations settings, R2 catalog metadata deletion, and MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
└──▷ TRY IT
Restrict Image Transformations to a specific allowed origin on a zone to prevent unauthorized image resizing from third-party domains.
copy
$ curl -X PUT 'https://api.cloudflare.com/client/v4/zones/{zone_id}/settings/transformations_allowed_origins' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' \
--data '{"value": ["https://example.com"]}' Enable C2PA content credentials on image transformations for a zone to embed provenance provenance Evidence recording where a software artifact came from and how it was built, including its source and build process. It helps a consumer check that the artifact matches a trusted build.
copy
$ curl -X PUT 'https://api.cloudflare.com/client/v4/zones/{zone_id}/settings/transformations_c2pa' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' \
--data '{"value": "on"}' Clean up stale R2 catalog metadata for a decommissioned bucket.
copy
$ curl -X DELETE 'https://api.cloudflare.com/client/v4/accounts/{account_id}/r2-catalog/{bucket_name}/delete' \
-H 'Authorization: Bearer <API_TOKEN>'
Adds GET /accounts/{account_id}/settings/transformations to list Image Resizing configurations for an account. Adds GET /zones/{zone_id}/settings/transformations_allowed_origins and PUT /zones/{zone_id}/settings/transformations_allowed_origins to read and change the Image Transformations Allowed Origins setting per zone. Adds GET /zones/{zone_id}/settings/transformations_c2pa and PUT /zones/{zone_id}/settings/transformations_c2pa to read and change the Image Transformations C2PA (Content Credentials) setting per zone. Adds DELETE /accounts/{account_id}/r2-catalog/{bucket_name}/delete to remove R2 catalog metadata for a bucket. Adds API endpoints to update and delete an MCP Portal, and to read details, update, and delete an MCP Server MCP Server A process that exposes tools, resources, and prompts over Anthropic's Model Context Protocol, letting an AI agent call external APIs or local services through a standardised interface.
5 details in Everything
Cloudflare adds Workers AI models, pkg.* Gateway selectors, Access-on-Worker policies, and Realtime SFU SFU A Selective Forwarding Unit: a media server architecture that relays incoming WebRTC streams to other participants without decoding them, reducing server CPU cost and latency in multi-party video or data pipelines.
Gateway HTTP policies can now detect and control software package downloads across seven major package ecosystems using pkg.* selectors. Two new ways to protect Workers with Cloudflare Access: apply a policy to a single Worker across all its domains, or set a default policy for every Worker in an account. Realtime SFU DataChannels now support configurable unordered and partially reliable delivery for latency-sensitive applications. Artifacts now supports data localization, allowing repo data to be stored and processed only within a selected jurisdiction. Qwen 3.8 27B (Alibaba's 27-billion-parameter vision language model) is now available on Workers AI.
+1 more
show less
DeepSeek V4 Flash and Pro reasoning models are now available on Workers AI, the first models on the platform with a one-million-token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it.
6 details in Everything
Cloudflare adds Workers AI models, Access policy controls, package registry security, and Realtime SFU SFU A Selective Forwarding Unit: a media server architecture that relays incoming WebRTC streams to other participants without decoding them, reducing server CPU cost and latency in multi-party video or data pipelines.
Gateway HTTP policies can now detect and control software package downloads across seven major package ecosystems using pkg.* selectors. Two new ways to protect Workers with Cloudflare Access: apply a policy to a single Worker across all its domains, or set a default policy for every Worker in an account. Realtime SFU DataChannels now support configuring unordered and partially reliable delivery for latency-sensitive use cases. Data localization support for Artifacts, allowing repo data to be stored and processed only within a selected jurisdiction. Qwen 3.8 27B (Alibaba's 27-billion-parameter vision language model) is now available on Workers AI.
+1 more
show less
DeepSeek V4 Flash and Pro reasoning models are now available on Workers AI, as the first models on the platform with a full one-million-token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it.
6 details in Everything
Configure origin application settings for Cloudflare Tunnel in the dashboard
Aug 18, 2026
· release notes
Dashboard now supports configuring Cloudflare Tunnel origin settings (HTTP, TLS, Connection) via the UI
Adds Additional application settings section in the dashboard for managing HTTP, TLS, and Connection parameters for published application routes.
1 detail in Everything
WAF - WAF Release - Scheduled changes for 2026-08-24 (2026-08-17)
Aug 17, 2026
·
issue 049
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Adds rule ...1489d892 — HTTP/2 Request Smuggling - Request Body Anomaly detection, deploying in Log mode on 2026-08-24. Adds rule ...20646260 — XSS - JavaScript Event Handler Coercion - Headers detection, deploying in Log mode on 2026-08-24. Adds rule ...d706d517 — XSS - JavaScript Event Handler Coercion - Body detection, deploying in Log mode on 2026-08-24. Adds rule ...660886c8 — XSS - JavaScript Event Handler Coercion - URI detection, deploying in Log mode on 2026-08-24. Merges beta rule ...c293b926 (XSS, HTML Injection - Script Tag - Beta ) into the existing rule ...7b58420b (XSS, HTML Injection - Script Tag ) on 2026-08-24.
5 details in Everything
New us jurisdiction for R2 buckets guarantees US-only data residency
Adds support for a us jurisdiction to R2, guaranteeing bucket data is stored and processed within the United States. Provides a jurisdiction-specific S3 endpoint (https://<ACCOUNT_ID>.us.r2.cloudflarestorage.com) for creating and accessing buckets in the us jurisdiction.
2 details in Everything
Qwen 3.8 27B now available on Workers AI
Aug 17, 2026
· release notes
Workers AI now supports Qwen 3.8 27B for multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats.
Adds the @cf/qwen/qwen3.8-27b model to Workers AI for reasoning and function calling function calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions. Enables a 262,144 token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it.
2 details in Everything
Post-quantum key exchange for MX deployments
Aug 17, 2026
· release notes
Cloudflare Email Security now supports post-quantum post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA. SMTP SMTP The application-layer protocol used to send email between servers and from clients to servers; cyber tools use it to relay alerts, phishing simulations, or exfiltrated data over standard mail infrastructure.
Enables automatic X25519MLKEM768 hybrid key agreement on inbound MX and outbound delivery SMTP connections when the peer supports it.
1 detail in Everything
Cloudflare adds DeepSeek V4 1M-token models, package registry security, Worker-level Access policies, and FIDO2 FIDO2 The open standard behind passkeys and hardware security keys, where a website checks a signature from the user's device instead of a password. Because the key is bound to the site, phishing pages cannot use it. MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone.
└──▷ USE IT
Test Cloudflare Access-gated Worker handlers locally with a simulated authenticated identity, without deploying.
wrangler.jsonc
copy
// wrangler.jsonc
{
"dev": {
"access": {
"aud": "my-app",
"identity": {
"email": "admin@example.com"
}
}
}
}
Configure an Artifacts namespace restricted to EU data residency at creation time.
copy
$ curl --request POST \
'https://api.cloudflare.com/client/v4/accounts/$ACCOUNT_ID/artifacts/namespaces' \
--header 'Authorization: Bearer $CLOUDFLARE_API_TOKEN' \
--header 'Content-Type: application/json' \
--data '{"namespace": "my-eu-namespace", "jurisdiction": "eu"}'
Adds @cf/deepseek-ai/deepseek-v4-pro-0813 and @cf/deepseek-ai/deepseek-v4-flash-0731 to Workers AI, both with a full 1,048,576-token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. function calling function calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions. Adds ctx.access and ctx.access.getIdentity() to Worker request context so authenticated requests expose the user's email, name, and groups without manual JWT JWT An open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object passed between parties. Cyber tools use it to verify identity and permissions without querying a central session store. Adds an access block inside the dev section of wrangler.jsonc to simulate Cloudflare Access identities locally — set aud, email, and related fields; remove the block to simulate unauthenticated requests. Adds pkg.ecosystem, pkg.name, pkg.version, pkg.namespace, and pkg.purl selectors to Cloudflare Gateway HTTP policies, enabling allow/block rules on software package downloads across npm, PyPI, RubyGems, Cargo, Go, Maven, and NuGet NuGet Microsoft's package manager for .NET, hosting a public registry of reusable libraries so tools can pull in dependencies without bundling or manually maintaining third-party code. Adds ordered, maxRetransmits, and maxPacketLifeTime fields to the Realtime SFU SFU A Selective Forwarding Unit: a media server architecture that relays incoming WebRTC streams to other participants without decoding them, reducing server CPU cost and latency in multi-party video or data pipelines. POST /v1/apps/$APP_ID/sessions/$SESSION_ID/datachannels/new), enabling unordered and partially-reliable delivery modes.
+7 more
show less
Adds jurisdiction field to the Artifacts namespace API (POST /api.cloudflare.com/client/v4/accounts/$ACCOUNT_ID/artifacts/namespaces), supporting eu and us values for data localization; jurisdictions are immutable after namespace creation. Adds ssh_fido2_key and piv_key as supported MFA methods in application-level and policy-level settings for infrastructure applications via independent FIDO2 MFA. Enables attaching an Access policy to a Worker itself (rather than individual routes/domains), so all associated domains, Custom Domains, workers.dev URLs, and preview URLs are covered automatically. Adds a global 'protect all Workers by default' mode, with per-Worker bypass exemptions for publicly accessible Workers. Adds an Access tab in the Workers & Pages dashboard section for viewing and managing all Worker-level Access policies. Promotes Certificate Transparency Certificate Transparency A public, append-only log system maintained by various operators (Google runs several) that records every TLS certificate issued, letting anyone audit CAs for misissued or rogue certificates. Adds a Blocked content area under Policies & rules in Cloudflare Email Security, allowing administrators to define plaintext or regex rules scoped to message subject, body, or both; available on Enterprise and Enterprise + PhishGuard plans.
12 details in Everything
You can now enable Access on a Worker or all Workers at once
Aug 14, 2026
· release notes
Cloudflare Workers now supports Access policy attachment at the Worker level with local testing via wrangler.
Attach an Access policy directly to a Worker so that all associated domains and preview URLs are automatically protected Make all Workers private by default, requiring sign-in for every existing and newly created Worker with a Worker-level bypass option Access the authenticated user identity in code via ctx.access.getIdentity() which returns email, name, and groups without manual JWT JWT An open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object passed between parties. Cyber tools use it to verify identity and permissions without querying a central session store. Test Access policies locally using wrangler dev by adding a dev block to wrangler.jsonc with access.dev configuration View and manage all Worker Access policies in the Access tab of the Workers & Pages section in the dashboard
5 details in Everything
DeepSeek V4 Flash and Pro now available on Workers AI
Aug 14, 2026
· release notes
DeepSeek V4 Flash and Pro now available on Workers AI with million-token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it.
Adds @cf/deepseek-ai/deepseek-v4-pro-0813 model to Workers AI for long-context agentic workflows Adds @cf/deepseek-ai/deepseek-v4-flash-0731 model as a faster, lower-cost option with enhanced agentic capabilities Enables reasoning mode and function calling function calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions.
3 details in Everything
Detect and control software package downloads with package registry security
Aug 13, 2026
· release notes
Cloudflare Gateway adds package registry security to detect and control software downloads
Gateway detects package downloads for npm, PyPI, RubyGems, Cargo, Go, Maven, and NuGet NuGet Microsoft's package manager for .NET, hosting a public registry of reusable libraries so tools can pull in dependencies without bundling or manually maintaining third-party code. Adds pkg.ecosystem, pkg.name, pkg.version, pkg.namespace, and pkg.purl selectors for HTTP policies. pkg.purl selector is available in the API only.
3 details in Everything
Oracle Cloud Infrastructure Object Storage support in Cloud Connector
Aug 13, 2026
· release notes
Cloudflare Cloud Connector adds support for Oracle Cloud Infrastructure Object Storage as a new provider.
Adds oci_storage as a supported provider value in Cloud Connector rules to route traffic to OCI OCI Open Container Initiative standard, maintained by the Linux Foundation, defining the image format and runtime spec that container tools share so images built once run anywhere OCI-compliant. Enables routing to OCI buckets using Amazon S3 Compatibility API with path-style or virtual-hosted endpoint formats
2 details in Everything
Certificate Transparency Monitoring is now Generally Available
Aug 13, 2026
· release notes
Certificate Transparency Certificate Transparency A public, append-only log system maintained by various operators (Google runs several) that records every TLS certificate issued, letting anyone audit CAs for misissued or rogue certificates.
Alerts for certificates issued on your behalf (Universal SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination. Alert emails provide structured certificate details and a direct link to manage CT Monitoring in the dashboard
2 details in Everything
Data localization support for Artifacts
Aug 13, 2026
· release notes
Artifacts namespaces now support jurisdiction field for data localization (EU/US)
Adds jurisdiction field to the Artifacts namespace creation API to enforce EU or US data residency Sets eu or us as the valid values for the new jurisdiction parameter
2 details in Everything
Cloudflare Status page rebuilt with independent notifications, Markdown API, and separate incident/maintenance feeds
└──▷ TRY IT
Fetch current Cloudflare status in Markdown so an AI agent or script can parse it without HTML scraping.
copy
$ curl -H "Accept: text/markdown" https://www.cloudflarestatus.com/locations
New notification system on www.cloudflarestatus.com delivers alerts independently of Cloudflare infrastructure via email, webhook, Slack, Discord, or Google Chat — fires even when Cloudflare itself is down. Every page on www.cloudflarestatus.com returns Markdown when requested with Accept: text/markdown, enabling AI agents to read current status without parsing HTML. Separate RSS and Atom feeds for incidents and maintenance: https://www.cloudflarestatus.com/api/v3/incidents.rss, https://www.cloudflarestatus.com/api/v3/incidents.atom, https://www.cloudflarestatus.com/api/v3/maintenance.rss, and https://www.cloudflarestatus.com/api/v3/maintenance.atom — subscribe to one without the other.
3 details in Everything
Cloudflare adds custom email content blocking rules, GA hostname routing with new IP range, and Sandbox SDK 1.0 preview
└──▷ HOW TO FIND IT
Block targeted phishing phrases in email subjects and bodies using a custom regex rule before any message reaches user inboxes.
📍 In the Cloudflare dashboard, go to Email Security › Policies & rules › Blocked content, click Add rule, set match type to regular expressions , enter your pattern (e.g. urgent.*wire transfer), set search location to subject and body , then use the built-in regular expression checker to validate against sample text before saving.
Install the Sandbox SDK 1.0 preview to start new projects on the unified exec interface and RPC RPC Remote Procedure Call, a protocol that lets a program execute a function on another machine as if it were local, giving cyber tools a structured way to communicate across processes or hosts without managing raw sockets.
copy
$ npm i @cloudflare/sandbox@next
New Blocked content area under Policies & rules in Cloudflare Email Security lets admins define plaintext or regular expression rules to block messages by subject, body, or subject and body; matching messages receive a malicious disposition and are blocked from inboxes. Available on Enterprise and Enterprise + PhishGuard plans. Built-in regular expression checker in the Blocked content UI lets you validate patterns against sample text before saving to reduce false positives. Hostname routing is now generally available in Cloudflare One, enabling traffic routing by private hostname (e.g. wiki.internal.local) or public hostname (e.g. bank.example.com) across Cloudflare Tunnel connectors and Mesh nodes without managing static IP lists. Sandbox SDK 1.0 preview is available under the npm @next tag (@cloudflare/sandbox@next) with a unified sandbox.exec() interface for both short commands and long-running services, RPC-only transport, and createTerminal/connect for interactive PTY sessions.
4 details in Everything
└──▷ BREAKING ON UPGRADE
! Sandbox SDK 1.0 (@next) removes session execution — shell state is no longer maintained between executions; each sandbox.exec() launch is independent. Pass cwd explicitly or combine multi-step logic in a single shell command.! Sandbox SDK 1.0 (@next) removes SANDBOX_TRANSPORT, the transport option on getSandbox() , and setTransport() — RPC is now the only transport.
Cloudflare adds email content blocking rules, hostname routing GA, and WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Adds blocked content rules for Email Security that block emails based on subject or body content using plaintext or regular expression matching. Releases Cloudflare WAF managed rulesets update (2026-08-11).
2 details in Everything
Cloudflare adds email content blocking rules, hostname routing GA, and WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Adds blocked content rules in Email Security to block emails by subject or body content using plaintext or regular expression matching. Releases updated Cloudflare WAF managed rulesets (2026-08-11).
2 details in Everything
└──▷ BREAKING ON UPGRADE
! Hostname routing initial resolved IPs are moving from the CGNAT range to a public Cloudflare IP range — firewall or routing rules that reference the previous CGNAT addresses may need to be updated.
MCP protocol detection and AI Security dashboard
Aug 12, 2026
· release notes
Cloudflare Gateway adds MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds experimental.is_mcp selector to HTTP policies for filtering Model Context Protocol Model Context Protocol Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Introduces an AI security report dashboard under Insights & Logs > Dashboards showing MCP request volume, users, servers, and policy summaries
2 details in Everything
Independent MFA supports FIDO2 for infrastructure applications
Aug 12, 2026
· release notes
Cloudflare Access now supports independent MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. FIDO2 FIDO2 The open standard behind passkeys and hardware security keys, where a website checks a signature from the user's device instead of a password. Because the key is bound to the site, phishing pages cannot use it.
Adds ssh_fido2_key and piv_key options to application-level and policy-level MFA settings for Infrastructure applications
1 detail in Everything
Block emails by content with blocked content rules
Aug 12, 2026
· release notes
Cloudflare Email Security adds user-defined blocked content rules via UI for Enterprise tiers
Adds a Blocked content area under Policies & rules where admins can define plaintext or regex patterns to match against email subject, body, or both. Includes a built-in regular expression checker to validate patterns against sample text before saving.
2 details in Everything
Traffic Source selector in Gateway policies
Aug 12, 2026
· release notes
Gateway HTTP and Network policies now support traffic source and browser isolation selectors via net.onramp.type and net.is_isolated.
Adds Traffic Source selector to Gateway HTTP and Network policies, enabling targeting of on-ramp methods like device_client, mesh, cloudflare_wan, clientless_rdp, proxy_endpoint, agentless_biso, and mcp_portal. Adds Browser Isolation selector to Gateway HTTP and Network policies, using the net.is_isolated field to apply policy behavior specifically to isolated sessions.
2 details in Everything
Agent Lee now exports generated code to a temporary git repo via a one-time clone command
Adds Copy clone command UI action in Agent Lee export card to download generated project files Creates a temporary Cloudflare-managed git repository (up to 50 files, 2 MB total) for exported Agent Lee code
2 details in Everything
Cloudflare launches R2 Data Catalog: a managed Apache Iceberg REST catalog Apache Iceberg REST catalog A standard HTTP API specification for querying and managing an Iceberg table catalog, letting cyber tools from different vendors discover, read, and write Iceberg metadata without vendor-specific integrations.
Introduces R2 Data Catalog, a managed Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS. Supports ACID transactions, optimized metadata indexing, and full schema evolution (add, rename, delete columns without rewriting data) via the open Apache Iceberg table format. Enables cross-cloud and cross-region analytical workloads — including log analytics, business intelligence, and data pipelines — with no egress fees under R2's zero-egress model.
3 details in Everything
Cloudflare R2 gains a managed Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS.
New R2 Data Catalog turns any R2 bucket into a managed Apache Iceberg catalog queryable by engines like Spark, Snowflake, and R2 SQL — no separate catalog infrastructure required.
1 detail in Everything
Cloudflare Sandbox adds outbound traffic control and Cloudflare Skills for coding agents, plus a @cloudflare/sandbox@next 1.0 preview SDK.
Supports blocking, allowing, and intercepting outbound HTTP from sandboxes, with the ability to inject authorization headers in outbound handlers to keep credentials inside the Worker. Adds Cloudflare Skills for coding agents, with three install targets: sandbox-stable for the current stable package, sandbox-next for @cloudflare/sandbox@next (recommended for new projects), and sandbox-migrate-to-next to port existing apps. Introduces @cloudflare/sandbox@next as a 1.0 preview SDK, enabling early adoption of the upcoming Sandbox SDK 1.0 release.
3 details in Everything
Cloudflare Workers AI adds ByteDance Seedance 2.5, a 30-second audio-video generation model with reference control and editing.
Cloudflare adds Tunnel live log streaming, MySQL in Hyperdrive GA, Turnstile Spin GA, unified AI billing, Mesh Docker/K8s images, and new Radar BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
└──▷ USE IT
Connect a Workers function to a MySQL database via Hyperdrive using the GA mysql2 integration.
javascript
copy
import { createConnection } from 'mysql2/promise';
export default {
async fetch(request, env, ctx) {
const connection = await createConnection({
host: env.HYPERDRIVE.host,
user: env.HYPERDRIVE.user,
password: env.HYPERDRIVE.password,
database: env.HYPERDRIVE.database,
port: env.HYPERDRIVE.port,
disableEval: true, // Required for Workers compatibility
});
const [results, fields] = await connection.query('SHOW tables;');
ctx.waitUntil(connection.end());
return new Response(JSON.stringify({ results, fields }), {
headers: { 'Content-Type': 'application/json' },
});
},
};
Route a Workers AI inference request through AI Gateway for observability, caching, and unified billing using the gateway option.
javascript
copy
const response = await env.AI.run(
'@cf/zai-org/glm-5.2',
{ messages: [{ role: 'user', content: 'What is the capital of France?' }] },
{ gateway: { id: 'default' } }
);
Retrieve AS-level BGP path segments toward Tier-1 networks for a specific ASN ASN Autonomous System Number — a globally unique identifier assigned by regional internet registries to a network operator, letting routing protocols distinguish which organization controls a block of IP addresses.
copy
$ curl 'https://api.cloudflare.com/client/v4/radar/bgp/routes/paths/13335?collector=route-views.oregon' \
-H 'Authorization: Bearer <API_TOKEN>'
Adds wrangler turnstile widget create CLI command to create a Turnstile widget and return the sitekey and secret for manual frontend/siteverify wiring. New Live logs tab under Networking > Tunnels > (tunnel detail view) in the Cloudflare dashboard streams real-time logs from single or multiple cloudflared connectors, with filtering by log level, event type (HTTP, TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. UDP UDP A network protocol that sends individual messages without guaranteeing delivery or order. Applications trade built-in reliability for less overhead and can add their own recovery. cloudflared internal), and HTTP method. New /bgp/routes/paths/{asn} Radar BGP API endpoint returns ordered AS path segments an AS uses to reach Tier-1 networks, with collector parameter to scope to a single RouteViews collector. New /bgp/routes/upstreams/{asn}/timeseries Radar BGP API endpoint returns the share of an AS's observed paths per upstream over time, with limit and ipVersion parameters. MySQL support in Hyperdrive is now generally available — connect from Workers using mysql2/promise via env.HYPERDRIVE.host, .user, .password, .database, and .port binding properties, with no code changes required for existing drivers, ORMs, or query builders.
+8 more
show less
Workers AI and AI Gateway now support unified billing via a Workers AI billing setting on the gateway set to Unified Billing , allowing prepaid AI Gateway credits to pay for Workers AI inference with a shared credit balance. Routing Workers AI requests through AI Gateway now supports a gateway: { id: 'default' } option in env.AI.run() calls; using 'default' auto-creates a gateway on the first authenticated request. Three frontier Workers AI models — @cf/moonshotai/kimi-k2.6, @cf/moonshotai/kimi-k2.7-code, and @cf/zai-org/glm-5.2 — are now accessible without the Workers Paid plan when billed via AI Gateway credits, at 50 requests per minute per account per model. Cloudflare Mesh nodes can now run as Docker containers via the cloudflare/mesh image on Docker Hub, supporting amd64 and arm64 architectures, Docker Compose, Kubernetes StatefulSet, Kubernetes sidecar, and CI/CD pipeline deployment patterns. Turnstile Spin is now generally available, offering AI-agent-assisted widget setup and server-side siteverify wiring via the Turnstile dashboard (Set up with Spin ), wrangler turnstile widget create, or by pasting the Spin prompt into Claude Code, Cursor, Codex, OpenCode, or GitHub Copilot Chat. Turnstile Spin includes server-side siteverify insertion snippets for Next.js (App Router and Pages Router), Astro, SvelteKit, Hugo, and vanilla HTML. Cloudflare Radar adds AS-level connectivity graph and Upstream providers stacked-area chart to AS pages (e.g. AS13335), with a Show full paths toggle and ipVersion selector for IPv4/IPv6 IPv6 The current version of the Internet Protocol, standardized by the IETF, using 128-bit addresses to replace the exhausted IPv4 space. Cyber tools target it because modern networks run dual-stack or IPv6-only. Cloudflare Radar adds Radar Researcher, a beta AI-powered assistant for exploring Internet trends in plain language via voice or text, accessible from the header on any Radar page.
13 details in Everything
Cloudflare API adds queue message peek/purge endpoints, URL intelligence lookup, and dataset deletion.
└──▷ TRY IT
Inspect pending messages in a Cloudflare Queue without consuming them, useful for debugging or monitoring queue depth.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/{account_id}/queues/{queue_id}/messages/peek' \
-H 'Authorization: Bearer <API_TOKEN>'
New POST /accounts/{account_id}/queues/{queue_id}/messages/peek endpoint to inspect queued messages without consuming them. New GET /accounts/{account_id}/intel/url endpoint to retrieve URL intelligence data for a given URL. New endpoint to delete an account or zone dataset.
3 details in Everything
Cloudflare adds real-time Tunnel log streaming, MySQL in Hyperdrive GA, Turnstile Spin GA, unified Workers AI/AI Gateway billing, Mesh Docker support, and Radar upgrades.
Cloudflare Tunnel detail view in the dashboard now supports real-time log streaming, including multi-connector aggregated streaming with filtering. MySQL and MySQL-compatible databases are now generally available in Hyperdrive, enabling connections from Workers. Turnstile Spin is now generally available — create a widget from the dashboard, Wrangler, or an AI coding agent, with server-side token verification. Workers AI and AI Gateway unify model access: call Workers AI and third-party models through shared APIs, observability, and prepaid billing. Cloudflare Mesh can now run as a Docker container image, supporting Docker Compose, Kubernetes, and CI/CD environments.
+2 more
show less
Cloudflare Radar AS routing pages add a connectivity graph showing how a network reaches Tier-1 networks, plus a timeseries of upstream providers. Cloudflare Radar adds a Researcher beta for exploring Internet data in plain language and WebMCP support for browser-based AI agents.
7 details in Everything
Cloudflare adds live Tunnel log streaming, MySQL Hyperdrive GA, unified Workers AI/AI Gateway billing, and Radar Researcher beta
The Tunnel detail view in the Cloudflare dashboard now supports real-time log streaming, including multi-connector aggregated streaming with filtering. MySQL and MySQL-compatible databases are now generally available in Hyperdrive, enabling Workers to connect to MySQL backends. Workers AI and AI Gateway unify model access, observability, and prepaid billing across Workers AI and third-party models through shared APIs. Turnstile Spin is now generally available — create a Turnstile widget from the dashboard, Wrangler, or an AI coding agent, with server-side token verification. Cloudflare Mesh nodes can now run as Docker containers, supporting Docker Compose, Kubernetes, and CI/CD environments.
+3 more
show less
Cloudflare Radar AS routing pages add a connectivity graph showing how a network reaches Tier-1 networks, plus a timeseries of upstream providers carrying its routes. Cloudflare Radar now includes the Radar Researcher beta for exploring Internet data in plain language, and WebMCP support for browser-based AI agents. New Cloudflare One Client for Windows (version 2026.6.905.0) released.
8 details in Everything
Hostname routing is now generally available, with a new public IP range for initial resolved IPs
Aug 11, 2026
· release notes
Hostname routing GA and new default public IPv4 range for initial resolved IPs
Hostname routing is now generally available to route traffic by hostname across Cloudflare One connectors instead of static IP lists.New default public IPv4 range 172.64.128.0/20 and IPv6 IPv6 The current version of the Internet Protocol, standardized by the IETF, using 128-bit addresses to replace the exhausted IPv4 space. Cyber tools target it because modern networks run dual-stack or IPv6-only. 2606:4700:0cf1:4000::/64 for initial resolved IPs.
2 details in Everything
New Cloudflare Status page adds independent notifications, separate incident/maintenance feeds, and Markdown API support.
└──▷ USE IT
Fetch machine-readable status updates for AI agents or scripts without HTML parsing overhead.
shell
copy
curl -H "Accept: text/markdown" https://www.cloudflarestatus.com/locations
Subscribe exclusively to maintenance windows in a feed reader, ignoring incident updates.
copy
$ https://www.cloudflarestatus.com/api/v3/maintenance.atom
Adds Accept: text/markdown header support to return raw Markdown content from the status page endpoints instead of HTML Adds separate RSS/Atom feed endpoints for incidents (.../api/v3/incidents.rss) and maintenance (.../api/v3/maintenance.rss) to allow independent subscription Adds independent notification system supporting email, webhook, Slack, Discord, and Google Chat subscriptions that function even during Cloudflare outages
3 details in Everything
Turnstile - Turnstile Spin is now generally available (2026-08-10)
Aug 10, 2026
·
issue 042
Turnstile Spin is GA: create widgets and wire siteverify via dashboard, Wrangler CLI, or AI coding agent.
└──▷ TRY IT
Quickly scaffold a Turnstile widget from the terminal and get the credentials needed to wire siteverify by hand.
copy
$ wrangler turnstile widget create
Adds wrangler turnstile widget create CLI command to create a Turnstile widget and print the sitekey and secret for manual frontend and siteverify integration. New Set up with Spin flow in the Turnstile dashboard lets you enter domains, generate a widget, and receive a sitekey, secret, and agent prompt in one step. AI coding agent path supports pasting the Spin prompt into Claude Code, Cursor, Codex, OpenCode, or GitHub Copilot Chat — agent fetches the skill, creates the widget, embeds it, and wires siteverify automatically. Spin includes frontend insertion snippets for Next.js (App Router and Pages Router), Astro, SvelteKit, Hugo, and vanilla HTML; proposes a generic pattern for other frameworks with a confirmation step. Automated validation step runs a real Turnstile token through the protected endpoint to confirm it passes, then replays the token to confirm the endpoint rejects it on the second attempt, stopping with diagnostics on failure.
5 details in Everything
Stream live logs from Cloudflare Tunnel in the dashboard
Aug 10, 2026
· release notes
Live logs tab added to Cloudflare Tunnel dashboard for real-time debugging and filtering
Adds a Live logs tab in the Cloudflare dashboard's Networking > Tunnels section for real-time log streaming from single or multiple connectors. Enables filtering of live tunnel logs by log level, event type, and HTTP method directly in the dashboard UI.
2 details in Everything
Cloudflare unifies Workers AI + AI Gateway billing, launches Kitesurf browser, adds BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
└──▷ TRY IT
Take a screenshot via Browser Run using Kitesurf to reduce CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/accounts/<ACCOUNT_ID>/browser-run/screenshot?browser=kitesurf' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' \
-d '{"url": "https://example.com"}' \
--output screenshot.png Index a site without a complete sitemap by using the discover parse type to follow links up to a set depth and page limit.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/<ACCOUNT_ID>/ai-search/instances' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' \
-d '{
"id": "my-ai-search",
"type": "web-crawler",
"source": "example.com",
"source_params": {
"web_crawler": {
"parse_type": "discover",
"discover_options": { "source": "links", "limit": 5000, "depth": 3 }
}
}
}' Query BGP upstream provider share for an AS over time, scoping to IPv6 IPv6 The current version of the Internet Protocol, standardized by the IETF, using 128-bit addresses to replace the exhausted IPv4 space. Cyber tools target it because modern networks run dual-stack or IPv6-only.
copy
$ curl 'https://api.cloudflare.com/client/v4/radar/bgp/routes/upstreams/13335/timeseries?limit=5&ipVersion=6' \
-H 'Authorization: Bearer <API_TOKEN>'
Adds browser=kitesurf parameter to Browser Run CDPCDP Cisco Discovery Protocol, a Cisco-proprietary Layer 2 protocol that advertises device identity, capabilities, and topology between directly connected Cisco gear, giving cyber tools a passive way to map network infrastructure. Quick Action endpoints to opt into Kitesurf, a new stateless browser using 3–7× less CPU and memory than Chromium for agentic workloads. Adds /bgp/routes/paths/{asn} Radar BGP API endpoint returning ordered AS path segments to Tier-1 networks, with collector parameter to scope to a single RouteViews collector. Adds /bgp/routes/upstreams/{asn}/timeseries Radar BGP API endpoint returning each direct upstream's share of observed paths over time, with limit and ipVersion parameters. Adds parse_type: discover for AI Search web-crawler data sources, with discover_options fields (source, limit, depth) to crawl pages beyond a sitemap by following links. Enables AI Search public endpoints on custom domains (e.g. https://search.example.com/search) with optional Cloudflare Access authentication in front of them.
+10 more
show less
Adds namespace-level public endpoints (https://ns-<NAMESPACE_ENDPOINT_ID>.search.ai.cloudflare.com/search and /chat/completions) that fan out across multiple AI Search instances via ai_search_options.instance_ids. Introduces unified billing between Workers AI and AI Gateway: set the gateway's Workers AI billing setting to Unified Billing so prepaid AI Gateway credits cover Workers AI inference in real time. Raises Workers AI frontier model rate limits to 50 requests per minute per account per model when billed through AI Gateway credits, up from 20 via standard Workers AI billing. Routes env.AI.run() Workers AI requests through an AI Gateway by specifying gateway: { id: "<gateway-id>" }, with "default" auto-creating a gateway on first authenticated request. Publishes the cloudflare/mesh Docker image on Docker Hub supporting amd64 and arm64, enabling Cloudflare Mesh nodes to run in Docker Compose, Kubernetes StatefulSet, Kubernetes sidecar, and CI/CD pipelines. Adds AS-level connectivity graph and Upstream providers widget to Cloudflare Radar AS pages (e.g. AS13335), with Show full paths toggle and IP version selector for IPv4/IPv6. Introduces Radar Researcher, a beta AI assistant on Cloudflare Radar with voice/text queries, interactive charts, searchable conversation history, shareable links, and an Explain with AI per-chart option. Adds WebMCP support to Cloudflare Radar, enabling browser-based AI agents to navigate Radar, search data, and use tools such as URL scanning and domain lookup. Introduces AI Gateway User Insights dashboard showing organization-wide AI cost, requests, tokens, and adoption, plus per-user spend, top models, providers, and cache hit rate. Adds anomalous-usage detection in AI Gateway User Insights, flagging sessions that exceed a user's p95 session cost baseline from the last 30 days and an organization-level threshold.
15 details in Everything
Workers AI and AI Gateway unify model access and billing
Aug 7, 2026
· release notes
Workers AI unifies with AI Gateway for shared billing, unified env.AI.run() binding, and /ai/ REST endpoints.
Adds a unified env.AI.run() binding that routes requests to both Workers AI and third-party providers Adds shared /ai/ REST endpoints with Cloudflare authentication for unified model access Enables prepaid AI Gateway credits for Workers AI inference via the Unified billing setting
3 details in Everything
Cloudflare Mesh now runs as a container image with built-in source NAT for Docker and Kubernetes
Introduces cloudflare/mesh container image on Docker Hub for running Cloudflare Mesh nodes in Docker Compose, Kubernetes, or OCI OCI Open Container Initiative standard, maintained by the Linux Foundation, defining the image format and runtime spec that container tools share so images built once run anywhere OCI-compliant. Adds support for amd64 and arm64 architectures to the Mesh container image Includes built-in source NAT in the Mesh container to route return traffic correctly without VPC VPC A logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware. Enables CI/CD integration by allowing the Mesh node to join, run tests against private infrastructure, and tear down automatically on container exit
4 details in Everything
AS-level connectivity and upstream providers on Cloudflare Radar
Aug 7, 2026
· release notes
Cloudflare Radar adds AS-level connectivity and upstream provider widgets plus corresponding /bgp routes API endpoints.
/bgp/routes/upstreams/{asn}/timeseries returns the share of an AS's observed paths carried by each direct upstream over time/bgp/routes/paths/{asn} Returns the ordered AS path segments an AS uses to reach the Tier-1 networks alongside peer count and contributing collectorsAdds Show full paths toggle and IP version selector (IPv4/IPv6 IPv6 The current version of the Internet Protocol, standardized by the IETF, using 128-bit addresses to replace the exhausted IPv4 space. Cyber tools target it because modern networks run dual-stack or IPv6-only. Adds Upstream providers stacked area chart widget showing transit changes per direct upstream
4 details in Everything
Radar Researcher beta and WebMCP support now available
Aug 7, 2026
· release notes
Radar beta adds AI-powered Researcher chat and WebMCP protocol support for browser-based agents.
Adds Radar Researcher beta, an AI assistant accessible from the header to ask questions via voice or text and view interactive charts based on API data. Supports WebMCP, a new protocol enabling browser-based AI agents to navigate Radar, search data, and execute tools like URL scanning and domain lookup.
2 details in Everything
Restart a Hyperdrive configuration from the dashboard
Aug 7, 2026
· release notes
Manual restart action for Hyperdrive pools via dashboard
MySQL support in Hyperdrive is now generally available
Aug 7, 2026
· release notes
Hyperdrive GA adds MySQL support for Cloudflare Workers
Load Balancing health notifications now resolve automatically
Aug 7, 2026
· release notes
Load Balancing health notifications now automatically resolve incidents via stateful recovery alerts
Adds automatic resolution of Load Balancing health alert incidents when a pool or endpoint recovers to a healthy state. Introduces stateful matching for Load Balancing health notifications, linking recovery events to original failure incidents. Enables delivery of recovery notifications alongside existing unhealthy notifications for Load Balancing pools and endpoints.
3 details in Everything
Cloudflare Workers AI adds FLUX 3 Video (text/image/video-to-video) and ElevenLabs v3 text-to-speech models.
Adds flux-3-video model from Black Forest Labs supporting text-to-video (t2v), image-to-video (i2v), and video-to-video (v2v) generation with synchronized audio, up to FHD resolution, and 5–20 second durations. Adds eleven-v3 model from ElevenLabs for expressive, natural text-to-speech generation with advanced voice control.
2 details in Everything
Cloudflare adds AI Gateway User Insights, identity-aware spend controls, agent tracing, Vectorize 20M-vector limit, and CI/CD for Artifacts repos
└──▷ USE IT
Automatically trigger a build-test-deploy pipeline whenever code is pushed to an Artifacts repo, with dependency caching keyed to the lockfile.
toml
copy
// wrangler.toml
[[triggers.events]]
type = "cf.artifacts.repo.pushed"
[triggers.events.filter]
namespace = "CI"
repoName = "my-repo"
[triggers.events.target]
scriptName = "my-ci-worker"
workflowName = "ci-workflow"
Instrument AI SDK v7 calls with agent tracing and enable payload recording for a booking agent in a Workers app.
javascript
copy
import * as ai from "ai";
import { wrapAISDK } from "agents/observability/ai";
const tracedAI = wrapAISDK(ai, { storeMessages: true, storeTools: true });
await tracedAI.generateText({
model,
prompt: "Find an available appointment",
runtimeContext: { agentId: "booking-agent-production", conversationId: "conversation-123" },
telemetry: { functionId: "booking-agent", includeRuntimeContext: { agentId: true, conversationId: true } }
});
Enable agent tracing in local development so the Local Explorer API and browser UI capture spans and logs for every Worker invocation.
toml
copy
# wrangler.toml
[observability.traces]
enabled = true
Adds cf.user_id to AI Gateway request metadata when traffic flows through a Cloudflare Access-protected custom domain, enabling identity-aware spend limits, log filtering, and routing without passing user IDs from the client. Adds cf.artifacts.repo.pushed Wrangler trigger event so a CI Workflow fires automatically on every Artifacts repo push; configure via triggers.events[].type, filter.namespace, filter.repoName, target.scriptName, and target.workflowName in wrangler.toml. Adds cache.inputs option to ci.runner() in @cloudflare/ci SDK to reuse installed dependencies across sandboxed CI steps when the lockfile (e.g. pnpm-lock.yaml or bun.lock) is unchanged. Introduces wrapAISDK() from agents/observability/ai to instrument AI SDK v6 and v7 calls with agent traces; accepts storeMessages and storeTools options (off by default) to control payload recording. Enables agent tracing in Wrangler via [observability.traces] enabled = true config key, capturing per-turn model calls, tool runs, approvals, token usage, and Workers runtime operations for Think, Flue, and AI SDK applications.
+7 more
show less
Exposes a read-only Local Explorer API at /cdn-cgi/explorer/api (serving an OpenAPI OpenAPI A vendor-neutral specification for describing REST APIs in a machine-readable format, maintained by the OpenAPI Initiative. Cyber tools use it to auto-generate clients, documentation, and validation from a single source of truth. wrangler dev / vite dev so AI agents and humans can query structured OpenTelemetry OpenTelemetry An open standard and set of tools for collecting traces, metrics and logs from applications. It lets services export observability data without tying instrumentation to one monitoring vendor. Adds new Eager redirect cookie setting to Cloudflare Access self-hosted applications, controlling whether CF_Authorization cookies are set preemptively across all public hostnames (on by default for new applications); previously behavior was fixed by hostname count. AI Gateway User Insights dashboard surfaces organization-wide spend totals (cost, requests, tokens, adoption) and per-user drill-downs (top models, providers, cache hit rate), with anomaly detection that baselines each user's p95 session cost over the last 30 days and flags sessions exceeding that baseline and an organization-level threshold. Vectorize indexes now support up to 20 million vectors per index (doubled from 10 million), at up to 1,536 dimensions per vector at 32-bit precision. Adds a Create Account button to the Cloudflare dashboard account switcher, allowing users to create up to 5 standalone Free accounts (requires ≥7 days of account tenure). WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. SSRF - Cloud rule action from Disabled to BLOCK.OAuth consent screens now display shield icons indicating application ownership and domain verification status (green filled = Cloudflare-owned; blue outlined = third-party with verified domain; amber filled = third-party without verified domain).
12 details in Everything
Cloudflare API gains sinkhole management, Pages tails/assets, BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
└──▷ TRY IT
Stream live logs from a Pages deployment to debug build or runtime issues in real time.
copy
$ curl -X POST "https://api.cloudflare.com/client/v4/accounts/<account_id>/pages/projects/<project_name>/deployments/<deployment_id>/tails" \
-H "Authorization: Bearer <API_TOKEN>" \
-H "Content-Type: application/json" Retrieve BGP upstream composition over time for an ASN ASN Autonomous System Number — a globally unique identifier assigned by regional internet registries to a network operator, letting routing protocols distinguish which organization controls a block of IP addresses.
copy
$ curl "https://api.cloudflare.com/client/v4/radar/bgp/routes/upstreams/13335/timeseries" \
-H "Authorization: Bearer <API_TOKEN>"
Adds GET /zones/{zone_id}/custom_hostnames/quota to retrieve the custom hostname quota for a zone. Adds GET /zones/{zone_id}/dnssec/zsk to list DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit. Adds POST /accounts/{account_id}/addressing/prefixes/{prefix_id}/validate to validate an IP prefix. Adds GET /accounts/{account_id}/billable-usage/info and GET /accounts/{account_id}/billable-usage (Version 1, Alpha) for retrieving account billable usage data. Adds full sinkhole CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. GET, POST, PUT, and DELETE on /accounts/{account_id}/intel/sinkholes/{sinkhole_id} for DNS sinkhole DNS sinkhole A DNS server configured to return false responses for malicious or unwanted domains, redirecting traffic to a controlled address instead of the real destination, so analysts can detect and block infected hosts.
+8 more
show less
Adds ingress rule management for sinkholes: POST /zones/{zone_id}/intel/sinkholes/{sinkhole_id}/ingresses, plus GET, PUT, and DELETE on /zones/{zone_id}/intel/sinkholes/{sinkhole_id}/ingresses/{ingress_id}. Adds GET /accounts/{account_id}/pages/projects/{project_name}/upload-token to retrieve a Pages project upload token. Adds Pages deployment tail endpoints: POST /accounts/{account_id}/pages/projects/{project_name}/deployments/{deployment_id}/tails and DELETE .../tails/{tail_id} for real-time log streaming. Adds Pages asset management endpoints: PUT /pages/assets/upsert-hashes, POST /pages/assets/check-missing, and POST /pages/assets/upload. Adds GET and PUT /accounts/{account_id}/zerotrust/subnets/initial_resolved_ip/{address_family} to retrieve and update the Zero Trust initial resolved IP subnet. Adds GET /radar/bgp/routes/upstreams/{asn}/timeseries for upstream composition time-series data per ASN. Adds GET /radar/bgp/routes/paths/{asn} for tier-1 BGP path segments per ASN. Adds GET and PUT /zones/{zone_id}/precursor to retrieve and update the Zone Precursor configuration.
13 details in Everything
Cloudflare adds AI spend tracking with identity attribution, identity-aware AI Gateway controls, and 20M-vector Vectorize support.
New User Insights feature tracks AI spend per identity and flags anomalous usage that may signal a security risk. Identity-aware controls in AI Gateway let teams set spend limits, control model access, and filter logs using Cloudflare Access identity. Vectorize indexes now support up to 20 million vectors, up from the previous limit. Agent traces for Think, Flue, and AI SDK (instrumented by Agents SDK) now surface model calls, tool runs, approvals, token usage, and runtime operations per turn. Artifacts repos can now trigger a Workflow on every push to run CI checks and deploy to a Worker or User Worker.
+2 more
show less
OAuth consent screens now display publisher verification details inline so users can identify application owners before granting access. All users can create standalone Free accounts directly from the Cloudflare dashboard.
7 details in Everything
Cloudflare adds AI spend tracking with identity attribution, identity-aware AI Gateway controls, Vectorize 20M vector support, and more.
Adds User Insights for AI Gateway: track organization-wide AI spend, attribute it to identities, and flag anomalous usage that can signal a security risk. Identity-aware controls now available in AI Gateway: use Cloudflare Access identity to set spend limits, control model access, and filter logs. Agent traces for Think, Flue, and AI SDK instrumented by Agents SDK now show model calls, tool runs, approvals, token usage, and runtime operations per turn. Artifacts repos can now trigger a Workflow on push to run CI checks and deploy to a Worker or User Worker. All users can now create standalone Free accounts directly from the Cloudflare dashboard.
5 details in Everything
Introducing Kitesurf, an agent-first browser on Browser Run
Aug 6, 2026
· release notes
Introduces Kitesurf, a stateless browser on Browser Run that uses browser=kitesurf to reduce resource consumption.
Adds browser=kitesurf parameter to Browser Run CDP CDP Cisco Discovery Protocol, a Cisco-proprietary Layer 2 protocol that advertises device identity, capabilities, and topology between directly connected Cisco gear, giving cyber tools a passive way to map network infrastructure.
1 detail in Everything
AI Search makes it easier to build a search engine for your data
Aug 6, 2026
· release notes
Cloudflare AI Search introduces custom domains, Access auth, namespace aggregation, and sitemap-less crawling to simplify building data search engines.
└──▷ TRY IT
Configure a new AI Search instance to use the discover parse type for sites without sitemaps.
copy
$ curl -X POST "https://api.cloudflare.com/client/v4/accounts/<ACCOUNT_ID>/ai-search/instances" \
-H "Authorization: Bearer <API_TOKEN>" \
-H "Content-Type: application/json" \
-d '{
"id": "my-ai-search",
"type": "web-crawler",
"source": "example.com",
"source_params": {
"web_crawler": {
"parse_type": "discover",
"discover_options": { "source": "links", "limit": 5000, "depth": 3 }
}
}
}'
Serves AI Search endpoints from a custom domain owned by the user instead of only search.ai.cloudflare.com Allows Cloudflare Access service tokens to restrict who can query the AI Search endpoint Adds namespace-level aggregation via <NAMESPACE_ENDPOINT_ID>.search.ai.cloudflare.com with instance_ids fan-out Adds discover parse type for website data sources to crawl links when no complete sitemap exists
4 details in Everything
Identity-aware controls are now available in AI Gateway
Aug 5, 2026
· release notes
AI Gateway integrates with Cloudflare Access for identity-aware controls, spend limits, and user ID metadata.
Enables AI Gateway to integrate with Cloudflare Access to protect endpoints via policy enforcement Adds cf.user_id request metadata field populated with the verified Access user ID when traffic is routed through an Access-protected custom domain
2 details in Everything
Track AI spend and catch anomalous usage with User Insights
Aug 5, 2026
· release notes
New User Insights dashboard in AI Gateway for tracking spend and detecting anomalous usage
Adds a User Insights dashboard in AI Gateway to track organization-wide spend (cost, requests, tokens) and adoption. Enables drilling into individual user details including top models, providers, and cache hit rate via custom metadata or Cloudflare Access integration.
2 details in Everything
Improved publisher verification details on OAuth consent screens
Aug 5, 2026
· release notes
OAuth consent screens now show shield icons indicating app ownership and domain verification status
API surface changed: 263 deprecated
Build and deploy Artifacts repos on every push
Aug 4, 2026
· release notes
New cf.artifacts.repo.pushed trigger and ci.runner() API enable push-based CI/CD for Artifacts repos.
Adds the cf.artifacts.repo.pushed workflow trigger to automate builds on Artifacts repo pushes Introduces the @cloudflare/ci SDK with the ci.runner() function and cache.inputs option for dependency caching
2 details in Everything
Log in to Wrangler without a local callback server
Aug 4, 2026
· release notes
Wrangler 4.119.0 adds --device flag for wrangler login to support OAuth Device Authorization Grant OAuth Device Authorization Grant An OAuth 2.0 flow for devices with no browser, where the device shows a short code the user enters on a separate machine to approve access, letting CLI tools and headless services obtain tokens without a redirect URI.
└──▷ USE IT
Authenticate in a container or remote SSH session where localhost callbacks are blocked.
shell
copy
npx wrangler login --device
Node.js compatibility is now enabled by default
Aug 4, 2026
· release notes
Workers enables Node.js compatibility flags by default for compat dates on or after 2026-08-04
AI agents can debug Workers with local tracing
Aug 4, 2026
· release notes
wrangler dev and vite dev now capture local OpenTelemetry OpenTelemetry An open standard and set of tools for collecting traces, metrics and logs from applications. It lets services export observability data without tying instrumentation to one monitoring vendor.
wrangler dev and vite dev automatically capture structured OpenTelemetry traces during local Worker invocations.AI agents detect an active session and receive a terminal hint pointing to the Local Explorer API at /cdn-cgi/local/explorer/api for querying telemetry, traces, and logs. Local Explorer browser UI now displays spans, timing, attributes, and errors for handler calls, outbound fetch() calls, and binding calls.
3 details in Everything
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly.
Changes default action for the SSRF - Cloud rule from Disabled to Block in the Cloudflare Managed Ruleset
1 detail in Everything
Agent traces for Think, Flue, and AI SDK instrumented by Agents SDK
Aug 4, 2026
· release notes
Add Workers Tracing configuration key observability.traces.enabled and AI SDK wrapAISDK() for Agent trace observability
Adds the [observability].traces.enabled configuration key to Wrangler config files to turn on Workers tracing. Adds the wrapAISDK() function from the agents/observability/ai module for instrumenting AI SDK calls with agent traces. Adds storeMessages and storeTools boolean options to wrapAISDK() to control payload recording.
3 details in Everything
Vectorize indexes now support up to 20 million vectors
Aug 4, 2026
· release notes
Cloudflare Vectorize indexes now support up to 20 million vectors per index
Doubles Vectorize index capacity from 10 million to 20 million vectors
1 detail in Everything
Create Free accounts from the dashboard
Aug 4, 2026
· release notes
Adds Create Account button in the Cloudflare dashboard to create up to five Free accounts directly.
Control authorization cookies for multi-domain Access applications
Aug 3, 2026
· release notes
Cloudflare Access adds manual control over eager redirect cookies for multi-domain applications.
Adds the ability to toggle the Eager redirect cookie setting for Access applications to control CF_Authorization cookie distribution across multiple hostnames.
1 detail in Everything
See fallback pool traffic separately in load balancing analytics
Aug 3, 2026
· release notes
Cloudflare Load Balancing Analytics now separates fallback pool traffic with distinct labels in charts and views
Adds Fallback label to load balancing analytics entries (e.g., pool-name (Fallback)) for traffic ignored health checks
1 detail in Everything
Preview: @cloudflare/computer agent runtime
Aug 3, 2026
· release notes
Cloudflare introduces @cloudflare/computer, an agent runtime with virtual filesystem and hybrid execution backends.
Adds @cloudflare/computer npm package for open-source agent runtime Adds Workspace class from @cloudflare/computer to provide a virtual SQLite-backed filesystem within Durable Objects Supports Isolate runtime via just-bash and Dynamic Workers for fast execution Supports Container runtime via Cloudflare Containers mounted through FUSE FUSE A Linux kernel interface that lets userspace programs implement a filesystem without kernel code, maintained as part of the kernel project; tools use it to mount virtual or synthetic filesystems without requiring root or kernel modules.
4 details in Everything
Billing for Cloudflare Pipelines is now enabled for non-enterprise accounts. Costs are based on SQL transform volume ($0.04/GB) and sink output volume ($0.03-$0.06/GB). Workers Paid plans include 50 GB/month of included usage.
Billing is now enabled for R2 Data Catalog
Aug 3, 2026
· release notes
Cloudflare R2 Data Catalog billing enabled for non-enterprise accounts with usage-based pricing.
Enables R2 Data Catalog billing for non-enterprise accounts, allowing metadata requests and compaction to incur charges beyond the free tier.
1 detail in Everything
Python and JavaScript Workers can now call each other via RPC
Aug 3, 2026
· release notes
Cloudflare Workers now supports cross-language RPC RPC Remote Procedure Call, a protocol that lets a program execute a function on another machine as if it were local, giving cyber tools a structured way to communicate across processes or hosts without managing raw sockets.
Enables Python Workers to call methods in TypeScript or JavaScript Workers via the env.RPC binding object Enables JavaScript or TypeScript Workers to call methods in Python Workers via the env.PYTHON_RPC binding object Supports configuration of cross-language RPC targets using the services array in Wrangler configuration with binding, service, and entrypoint keys
3 details in Everything
R2 SQL billing is live for non-enterprise accounts, charging $0.0025 per GB of scanned compressed data with a 10GB monthly free tier.
Cloudflare adds Stream key rotation, AI Search SDK integrations, Browser Run human handoff, Gateway DNS TTL TTL Time to live, a limit on how long data remains valid or how far a packet can travel. Caches use a time limit; IP packets use a hop limit.
└──▷ TRY IT
Rotate compromised broadcast credentials for a Stream live input without changing its identifier.
copy
$ curl --request POST 'https://api.cloudflare.com/client/v4/accounts/{account_id}/stream/live_inputs/{live_input_identifier}/rotate_keys' --header 'Authorization: Bearer <API_TOKEN>' Profile a Worker's cold-start CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware.
copy
$ wrangler check startup Add grounded AI Search retrieval to a LangChain RAG RAG Retrieval-augmented generation: looking up relevant documents and adding them to the prompt before the model answers. It grounds responses in private or current data without retraining. hybrid search hybrid search Combining keyword search with semantic or vector search. The results use both exact term matches and similarity in meaning.
python
copy
from langchain_cloudflare import CloudflareAISearchRetriever
retriever = CloudflareAISearchRetriever(
account_id="ACCOUNT_ID",
api_token="API_TOKEN",
instance_name="knowledge-base",
retrieval_type="hybrid",
)
results = retriever.invoke("How do I configure Workers AI?")
Adds a rotate_keys API endpoint for Stream live inputs, revoking old broadcast credentials and returning fresh ones without changing the live input identifier; response now includes a keysRotatedAt field. Adds wrangler check startup bundle size reporting and CPU startup profiling — raw/compressed sizes and sampled/active/GC/idle time summary printed directly in the terminal. Adds AI Search integrations for Vercel AI SDK (ai-search-provider package), LangChain (CloudflareAISearchRetriever in langchain-cloudflare), and a new Cloudflare Agents SDK guide for stateful chat agents backed by AI Search. Sets Node.js 24.18.0 as the default runtime for Workers Builds; Node.js 22.23.2 also preinstalled. Cloudflare MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. /mcp endpoint accepts stateless requests from 2025 Streamable HTTP Streamable HTTP An MCP transport protocol that lets a client send JSON-RPC requests over HTTP POST while the server streams responses back using Server-Sent Events, replacing the older stdio and SSE transports for remote tool communication.
+3 more
show less
Browser Run adds structured Human in the Loop handoff via CDP CDP Cisco Discovery Protocol, a Cisco-proprietary Layer 2 protocol that advertises device identity, capabilities, and topology between directly connected Cisco gear, giving cyber tools a passive way to map network infrastructure. Cloudflare.handoff / Cloudflare.handoffComplete), enabling agents to formally pause for human intervention and resume automatically. Adds a maximum TTL setting for Cloudflare Gateway DNS caching, configurable at the account level (Traffic Settings) or per DNS location, capping upstream TTLs to accelerate policy change propagation. DoH DoH DNS over HTTPS, an IETF standard (RFC 8484) that tunnels DNS queries inside encrypted HTTPS traffic, making resolution indistinguishable from web traffic and bypassing traditional DNS-based monitoring. DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit.
8 details in Everything
└──▷ BREAKING ON UPGRADE
! Historical /sse URLs on Cloudflare MCP servers no longer serve the deprecated HTTP+SSE SSE Server-Sent Events, a browser API and HTTP-based protocol where a server pushes a stream of text events to a client over a single long-lived connection, giving tools a lightweight alternative to WebSockets for one-way real-time updates. ! DoH JSON API (application/dns-json) DNSSEC records now emit numeric algorithm identifiers (e.g., 8 instead of RSASHA256, 13 instead of ECDSAP256SHA256, 15 instead of ED25519) and numeric digest types (e.g., 2 instead of SHA-256SHA-256 A cryptographic hash function that turns data into a fixed 256-bit fingerprint. It is used to check integrity; hashing does not encrypt the original data. ! DoH JSON API (application/dns-json) data field format changes for CAA, NAPTR, RP, IPSECKEY, SVCB, HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate. \# <length> <hex>), now returns standard presentation format — consumers parsing hex encoding will break.! DoH JSON API (application/dns-json) HINFO data field now individually quotes each character-string (e.g., "\"Intel Xeon\" \"Linux\"" instead of "Intel Xeon Linux") — parsers expecting a single unquoted string will break.
Cloudflare One Client for Windows (version 2026.7.1210.1)
Jul 31, 2026
· release notes
Cloudflare One Client 2026.7.1210.1 adds protocol fallback and fixes MASQUE stall
Adds protocol order swapping after repeated connectivity-check failures to handle HTTP/3 HTTP/3 The third major version of HTTP, standardized by the IETF, which runs over QUIC instead of TCP, eliminating head-of-line blocking and reducing connection latency for faster, more resilient data transfer. Increases tolerance for large numbers of local domain fallback resolver IPs in configuration. Enables re-evaluation of device profile upon successful re-authentication.
3 details in Everything
Inspect Worker startup performance with Wrangler
Jul 31, 2026
· release notes
Wrangler 4.116.0 adds wrangler check startup to inspect Worker bundle sizes and local CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware.
Adds the wrangler check startup subcommand to report raw and compressed bundle sizes during analysis Adds a terminal summary of local CPU activity (sampled, active, garbage collection, idle time) during Worker startup via wrangler check startup Generates a worker-startup.cpuprofile file for detailed flamegraph analysis in Chrome DevTools or VS Code
3 details in Everything
Rotate Stream broadcast keys for live inputs
Jul 31, 2026
· release notes
Cloudflare Stream adds POST /rotate_keys endpoint for rotating live input broadcast credentials
Adds POST https://api.cloudflare.com/client/v4/accounts/{account_id}/stream/live_inputs/{live_input_identifier}/rotate_keys to rotate Stream live input broadcast keys without changing the live input identifier. New keysRotatedAt field in live input responses indicates when keys were last rotated, omitted for inputs never rotated.
2 details in Everything
Static OAuth client credentials for MCP server portals
Jul 31, 2026
· release notes
Adds static OAuth client credential configuration for MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds client_id and client_secret entry fields in the portal UI for manual OAuth credential input Supports custom OAuth endpoints, scopes, and token endpoint authentication methods (client_secret_post, client_secret_basic)
2 details in Everything
Browser Run adds a Playground to the Cloudflare dashboard
Jul 31, 2026
· release notes
Browser Run adds a Playground in the Cloudflare dashboard for testing Quick Actions without deploying code.
Enables output via the snapshot endpoint and screenshot/PDF capture directly from the Playground Adds HTML, Markdown, links, scraped data, and AI structured data extraction options Adds viewport, scale, timeout, selector wait, and device emulation configuration in the UI Adds Show Code export generating cURL, TypeScript SDK, Python, or Workers Binding snippets
4 details in Everything
Admins can turn on Code Mode by default for MCP portal users
Jul 30, 2026
· release notes
MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. code_mode API field for configuring Code Mode policies.
Adds the code_mode API field to MCP portal configuration with support for off, opt_in, default_on, and enforced values. Deprecates the previous allow_code_mode boolean in favor of the new policy-based approach.
2 details in Everything
Use AI Search with the Agents SDK, AI SDK, and LangChain
Jul 30, 2026
· release notes
New ai-search-provider package and CloudflareAISearchRetriever add direct AI Search integration with Vercel AI SDK and LangChain.
Adds the ai-search-provider npm package to expose AI Search as a provider for Vercel AI SDK v6, enabling instance.chat() in generateText/streamText calls and exposing instance.search() as a tool Adds CloudflareAISearchRetriever class to the existing langchain-cloudflare PyPI package as a new retriever backed by AI Search Publishes new guides in the Agents section for configuring AI Search with the Agents SDK, AI SDK, and LangChain
3 details in Everything
Cloudflare AI adds 13 new models: Anthropic Claude Opus 5, ByteDance video/image gen, ElevenLabs TTS/music, Gemini 3.5/3.6, Inkling MoE MoE A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token.
Adds Claude Opus 5 (Anthropic) with 1M-token context and adaptive reasoning for complex agentic coding and enterprise workloads. Adds Seedance 2.0 Mini (ByteDance) for high-volume text-to-video, image-to-video, reference video, and reference-audio background music generation. Adds Seedream 5 Pro (ByteDance) for high-quality image generation and editing with up to 10 reference images and 1K/2K/explicit pixel-size output controls. Adds three ElevenLabs text-to-speech models: Flash v2.5 (low-latency multilingual), Multilingual v2 (natural speech across many languages), and Turbo v2.5 (high-quality across 32 languages). Adds ElevenLabs Music v2 for composing songs and instrumental tracks from a prompt or detailed composition plan.
+5 more
show less
Adds Gemini 3.5 Flash-Lite, a low-latency multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. Adds Gemini 3.6 Flash for frontier-level intelligence at higher speed and lower cost, excelling at code generation, agentic execution, and spatial reasoning. Adds nano-banana-2-lite, Google's fastest Gemini image generation model for rapid image creation and iteration. Adds Inkling and Inkling-256K (Thinking Machines), open-weights hybrid MoE reasoning models with chain-of-thought chain-of-thought Intermediate reasoning a model writes out before its final answer. Reasoning models generate it automatically and it is often billed as extra output tokens. output_config.effort, tool use tool use A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions. Adds xAI Grok 4.5 with text and image input, function calling function calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions. structured outputs structured outputs Forcing a model's response to match a given format or JSON schema, so software can parse it reliably instead of hoping the text is well formed.
10 details in Everything
Run Devin AI coding sessions in isolated Cloudflare containers via Devin Outposts.
Supports deploying Devin Outposts on Cloudflare, running each Devin session in an isolated container for secure AI-assisted development.
1 detail in Everything
Cloudflare adds Gateway DNS max-TTL TTL Time to live, a limit on how long data remains valid or how far a packet can travel. Caches use a time limit; IP packets use a hop limit. MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly.
└──▷ HOW TO FIND IT
Cap DNS TTL at 60 seconds for a specific Gateway location so that newly blocked malicious domains take effect within one minute for all clients.
📍 In the Cloudflare dashboard, go to Gateway › DNS Locations › [your location] › Settings and set the Maximum TTL override to 60 seconds. To apply a default cap for all locations, go to Gateway › Traffic Policies › Traffic Settings › Proxy and inspection › Maximum DNS TTL.
Instrument a streaming Workers response with a custom span that stays open until the stream is fully consumed.
js
copy
import { tracing } from "cloudflare:workers";
export default {
async fetch(request) {
return tracing.startActiveSpan("stream-response", (span) => {
const encoder = new TextEncoder();
let timer;
const body = new ReadableStream({
start(controller) {
controller.enqueue(encoder.encode("Starting...\n"));
timer = setTimeout(() => {
controller.enqueue(encoder.encode("Complete.\n"));
controller.close();
span.setAttribute("stream.status", "complete");
span.end();
}, 1000);
},
cancel() {
if (timer !== undefined) clearTimeout(timer);
span.setAttribute("stream.status", "cancelled");
span.end();
},
});
return new Response(body, { headers: { "content-type": "text/plain" } });
});
},
};
Pause a browser automation agent at a login wall and let a human operator complete the login before the agent resumes.
js
copy
const cdp = await createCDPSession();
// Get Live View URL for the human operator
const { devtoolsFrontendUrl } = await cdp.send("Cloudflare.getLiveView", { mode: "tab" });
console.log(`Human input needed: ${devtoolsFrontendUrl}`);
// Request human intervention and wait for completion
const handoffComplete = new Promise((resolve) => cdp.once("Cloudflare.handoffComplete", resolve));
await cdp.send("Cloudflare.handoff", {
instructions: "Please log in with your credentials",
timeout: 600000,
});
const { success, reason } = await handoffComplete;
console.log(success ? "Handoff complete" : `Failed: ${reason}`);
Adds maximum TTL setting for Cloudflare Gateway DNS caching, capping upstream TTLs at account or per-location level to enforce faster policy propagation; two new DNS log fields (upstream_record_ttls and applied_max_ttl) are available in logs and Logpush datasets. New Workers runtime APIs tracing.startActiveSpan() and span.end() enable custom open-ended tracing spans that stay active beyond a single callback, supporting instrumentation of stream pipelines and other async workflows. Browser Run now supports structured Human in the Loop handoff via Cloudflare-specific CDP CDP Cisco Discovery Protocol, a Cisco-proprietary Layer 2 protocol that advertises device identity, capabilities, and topology between directly connected Cisco gear, giving cyber tools a passive way to map network infrastructure. Cloudflare.handoff, Cloudflare.getLiveView, Cloudflare.handoffComplete), letting agents formally pause for human intervention and resume automatically. Cloudflare MCP servers and Agents SDK v0.20.0 now support the MCP 2026-07-28 specification with stateless, sessionless request handling; new createMcpHandler factory serves both MCP 2026-07-28 and legacy clients from a single route. WAF adds new detection rules for Nuxt Server Island RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives. deserialization deserialization Turning stored or transmitted data back into objects a program can use. Unsafe handling of untrusted data can allow unexpected behavior or code execution. command injection command injection An attack that makes an application execute operating-system commands supplied through untrusted input. It often happens when input is passed unsafely to a shell.
+1 more
show less
1.1.1.1 DoH DoH DNS over HTTPS, an IETF standard (RFC 8484) that tunnels DNS queries inside encrypted HTTPS traffic, making resolution indistinguishable from web traffic and bypassing traditional DNS-based monitoring. application/dns-json) now returns human-readable presentation format for CAA, NAPTR, RP, IPSECKEY, SVCB, HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate.
6 details in Everything
└──▷ BREAKING ON UPGRADE
! DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit. RSASHA256 becomes 8, ECDSAP256SHA256 becomes 13, ED25519 becomes 15); DS digest types also change from mnemonic to numeric (e.g., SHA-256SHA-256 A cryptographic hash function that turns data into a fixed 256-bit fingerprint. It is used to check integrity; hashing does not encrypt the original data. 2).! The /sse endpoint on Cloudflare MCP servers no longer serves the deprecated HTTP+SSE SSE Server-Sent Events, a browser API and HTTP-based protocol where a server pushes a stream of text events to a client over a single long-lived connection, giving tools a lightweight alternative to WebSockets for one-way real-time updates. Streamable HTTP Streamable HTTP An MCP transport protocol that lets a client send JSON-RPC requests over HTTP POST while the server streams responses back using Server-Sent Events, replacing the older stdio and SSE transports for remote tool communication.
Cloudflare adds Gateway DNS TTL TTL Time to live, a limit on how long data remains valid or how far a packet can travel. Caches use a time limit; IP packets use a hop limit. MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
└──▷ USE IT
Instrument a stream pipeline in a Worker with a custom tracing span that outlives a single callback.
javascript
copy
const span = tracing.startActiveSpan('stream-processing');
try {
await processStream(request.body);
} finally {
span.end();
}
Adds maximum TTL setting for Cloudflare Gateway DNS caching, configurable at the account level and overridable per DNS location. New tracing.startActiveSpan() and span.end() runtime APIs let Workers developers write custom tracing spans for long-lived operations like stream pipelines. Browser Run now supports structured handoff, enabling automation scripts to formally request human intervention and resume when complete. Cloudflare MCP servers now support the MCP 2026-07-28 Specification with compatibility for 2025 Streamable HTTP Streamable HTTP An MCP transport protocol that lets a client send JSON-RPC requests over HTTP POST while the server streams responses back using Server-Sent Events, replacing the older stdio and SSE transports for remote tool communication. Agents SDK v0.20.0 adds client and server support for MCP 2026-07-28, including stateless Workers and compatibility with legacy MCP servers.
+2 more
show less
1.1.1.1 DoH DoH DNS over HTTPS, an IETF standard (RFC 8484) that tunnels DNS queries inside encrypted HTTPS traffic, making resolution indistinguishable from web traffic and bypassing traditional DNS-based monitoring. DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit. Wrangler's createTestHarness() API enables integration tests against a Worker's production build output from any Node.js test runner.
7 details in Everything
Cloudflare adds Gateway DNS max-TTL TTL Time to live, a limit on how long data remains valid or how far a packet can travel. Caches use a time limit; IP packets use a hop limit. MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
└──▷ USE IT
Instrument a Workers stream pipeline with a custom span that begins and ends outside a single callback.
js
copy
const span = tracing.startActiveSpan('process-stream');
await pipelineWork();
span.end();
Adds maximum TTL setting for Cloudflare Gateway DNS caching, configurable at the account level and overridable per DNS location. New tracing.startActiveSpan() and span.end() runtime APIs let Workers developers write custom tracing spans for operations that outlive a single callback, such as stream pipelines. Browser Run now supports structured handoff, enabling automation scripts to formally request human intervention and resume execution when complete. Cloudflare MCP servers now support the MCP 2026-07-28 Specification with compatibility for 2025 Streamable HTTP Streamable HTTP An MCP transport protocol that lets a client send JSON-RPC requests over HTTP POST while the server streams responses back using Server-Sent Events, replacing the older stdio and SSE transports for remote tool communication. Agents SDK v0.20.0 adds client and server support for MCP 2026-07-28, including stateless Workers and compatibility with legacy MCP servers.
+2 more
show less
Wrangler's createTestHarness() API enables integration tests to run against a Worker's production build output from any Node.js test runner. The 1.1.1.1 DoH DoH DNS over HTTPS, an IETF standard (RFC 8484) that tunnels DNS queries inside encrypted HTTPS traffic, making resolution indistinguishable from web traffic and bypassing traditional DNS-based monitoring. DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit.
7 details in Everything
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives.
Adds new detection rule Alibaba Fastjson JSONType Remote Code Execution - Body in the Cloudflare Managed Ruleset to block arbitrary system command execution via JSON deserialization deserialization Turning stored or transmitted data back into objects a program can use. Unsafe handling of untrusted data can allow unexpected behavior or code execution. Adds new detection rule Nuxt Server Island - RCE in the Cloudflare Managed Ruleset to block unauthenticated Remote Code Execution attacks exploiting Nuxt Server Islands components
2 details in Everything
Control Cloudflare Gateway DNS caching with a maximum TTL setting
Jul 28, 2026
· release notes
Cloudflare Gateway introduces DNS TTL TTL Time to live, a limit on how long data remains valid or how far a packet can travel. Caches use a time limit; IP packets use a hop limit.
Adds upstream_record_ttls and applied_max_ttl fields to DNS logs for visibility into capped TTLs Enables configuring a maximum DNS TTL cap at the account level under Traffic Policies > Traffic Settings > Proxy and inspection
2 details in Everything
Workers tracing — write custom spans with new startActiveSpan() and span.end() runtime APIs
Jul 28, 2026
· release notes
Cloudflare Workers adds startActiveSpan() and span.end() runtime APIs for long-running custom traces
Adds tracing.startActiveSpan() to the Workers runtime API Adds span.end() method to manually close active spans
2 details in Everything
Improved DoH JSON formatting for additional record types
Jul 28, 2026
· release notes
1.1.1.1 DoH DoH DNS over HTTPS, an IETF standard (RFC 8484) that tunnels DNS queries inside encrypted HTTPS traffic, making resolution indistinguishable from web traffic and bypassing traditional DNS-based monitoring. HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate.
1.1.1.1 DoH JSON API uses standard presentation format for CAA, NAPTR, RP, IPSECKEY, SVCB, HTTPS, TLSA, SSHFP, and OPENPGPKEY records instead of RFC 3597 hex encoding.1.1.1.1 DoH JSON API uses numeric DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit. 1.1.1.1 DoH JSON API individually quotes HINFO character-strings in the data field.
3 details in Everything
Cloudflare MCP servers support the new MCP 2026-07-28 Specification
Jul 28, 2026
· release notes
Cloudflare MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. /mcp endpoint.
/mcp endpoint accepts stateless requests from 2025 Streamable HTTP Streamable HTTP An MCP transport protocol that lets a client send JSON-RPC requests over HTTP POST while the server streams responses back using Server-Sent Events, replacing the older stdio and SSE transports for remote tool communication.
1 detail in Everything
Browser Run adds structured handoff for Human in the Loop
Jul 28, 2026
· release notes
Browser Run adds structured Human in the Loop handoff via new CDP CDP Cisco Discovery Protocol, a Cisco-proprietary Layer 2 protocol that advertises device identity, capabilities, and topology between directly connected Cisco gear, giving cyber tools a passive way to map network infrastructure.
Adds Cloudflare.handoff and Cloudflare.getLiveView CDP commands for Human in the Loop workflows Adds Cloudflare.handoffComplete CDP event to signal when human intervention is finished
2 details in Everything
Run integration tests against your Worker's production build
Jul 27, 2026
· release notes
Wrangler introduces createTestHarness() API for running integration tests against Workers locally.
Adds createTestHarness() function in Wrangler to start a local Worker server for integration testing Enables mocking outbound fetch() requests using Node.js libraries like MSW within the test harness Recommends createTestHarness() over unstable_startWorker() and unstable_dev() for new integration tests
3 details in Everything
Audit Logs v2 now includes Resource History with new UI tab and API endpoints to view change diffs
Adds a History tab in the Dashboard audit log entry view to see side-by-side diffs of resource changes. Adds GET /client/v4/accounts/{account_id}/logs/audit/{id}/history and GET /organizations/{organization_id}/logs/audit/{id}/history API endpoints to retrieve change history for an audit log entry.
2 details in Everything
Agents SDK adds MCP Specification 2026-07-28 support
Jul 27, 2026
· release notes
Cloudflare Agents SDK v0.20.0 adds MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. createMcpHandler and stateless servers.
Adds createMcpHandler factory in agents/mcp/server to run isolated, stateless MCP servers on Workers Enables clients to probe for MCP 2026-07-28 support using the server/discover endpoint and auto-fallback to legacy initialize handshake Exposes isLegacyRequest in @modelcontextprotocol/server to route traffic between stateless and legacy McpAgent handlers Deprecates the McpAgent class, freezing it as feature-complete while directing migration to the new factory pattern Updates OAuth callback validation to use v2 SDK issuer metadata discovery with persistent state across browser redirects
5 details in Everything
└──▷ BREAKING ON UPGRADE
! McpAgent is now feature-frozen and deprecated; servers depending on sessionful features must migrate using createMcpHandler or keep the legacy route active during transition
Sippy now supports Azure Blob Storage and S3-compatible storage providers
Jul 24, 2026
· release notes
Sippy now supports incremental migration from Azure Blob Storage and S3-compatible S3-compatible An object-storage API that mirrors Amazon S3's HTTP interface, so any client or cyber tool written for AWS S3 works unchanged against any compliant storage backend.
Enables copying objects to Cloudflare R2 on-demand as application requests them, avoiding upfront full-dataset migration or egress fees.
1 detail in Everything
Filter Durable Object logs and traces by instance ID
Jul 24, 2026
· release notes
Filter Durable Object logs and traces by instance ID using new fields
Logs for Durable Object requests now include the workers.durableObjectId field to filter logs for a specific instance OpenTelemetry OpenTelemetry An open standard and set of tools for collecting traces, metrics and logs from applications. It lets services export observability data without tying instrumentation to one monitoring vendor. cloudflare.durable_object.id attribute in root and child spans to isolate specific instances
2 details in Everything
Cloudflare adds Agents SDK MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ USE IT
Suppress Think's automatic MCP tool injection when you're managing MCP tools yourself through Code Mode, to avoid duplicate tool registration.
javascript
copy
import { Think } from "@cloudflare/think";
const result = await Think({
includeMcpTools: false,
waitForMcpConnections: true,
// ... other Think options
});
Allow an MCP server or custom host to discover and invoke a connector method on the Code Mode durable runtime without using the AI SDK.
javascript
copy
const matches = await runtime.search("create issue");
const docs = await runtime.describe(matches.results[0].path);
const outcome = await runtime.execute({
code: `async () => github.create_issue({ title: "Bug" })`
});
Adds includeMcpTools option to @cloudflare/think to opt out of Think's automatic MCP tool exposure when tools are managed externally (e.g., via Code Mode). Agents SDK MCP clients now reuse converted input/output schemas across model turns within a live connection, eliminating redundant JSON Schema-to-Zod conversions. Adds execute() , search() , and describe() methods to the @cloudflare/codemode durable runtime handle, enabling MCP servers and non-AI-SDK hosts to invoke Code Mode directly. Introduces Devin Outposts: run Devin agent sessions on Cloudflare-managed, container-isolated infrastructure via the Sandbox SDK. Deploys new WAF rules covering Next.js DoS (CVE-2026-64641), Next.js SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. SQL injection SQL injection An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does.
+2 more
show less
Enhances WAF generic protections against SSRF, Local File Inclusion (LFI), and Cross-Site Scripting (XSS XSS Cross-site scripting, an attack that runs malicious script in another user's browser through a trusted site. It can steal data or perform actions using the user's session. Introduces the Permission Groups API as the replacement for the deprecated Account Roles API, supporting API Token authorization and a new meta object with label and scopes in the response schema.
7 details in Everything
└──▷ BREAKING ON UPGRADE
! The Account Roles API is deprecated and replaced by the Permission Groups API; integrations must obtain Permission Group IDs from the new API and use them in Account Members API policies — legacy Role IDs must be remapped.! The PermissionGroup response replaces the legacy Role top-level description and permissions object (keyed by resource type with edit/read flags) with a meta object containing label and scopes; individual permissions are no longer returned as part of the permission group.
Cloudflare adds Agents SDK MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ USE IT
Suppress Think's automatic MCP tool injection when you're managing MCP tools yourself through Code Mode, to avoid duplicate tool registration.
javascript
copy
import { Think } from "@cloudflare/think";
const result = await Think({
includeMcpTools: false,
waitForMcpConnections: true,
// ... other Think options
});
Allow an MCP server or custom host to discover and invoke a connector method on the Code Mode durable runtime without using the AI SDK.
javascript
copy
const matches = await runtime.search("create issue");
const docs = await runtime.describe(matches.results[0].path);
const outcome = await runtime.execute({
code: `async () => github.create_issue({ title: "Bug" })`
});
Adds includeMcpTools option to @cloudflare/think to opt out of Think's automatic MCP tool exposure when tools are managed externally (e.g., via Code Mode). Agents SDK MCP clients now reuse converted input/output schemas across model turns within a live connection, eliminating redundant JSON Schema-to-Zod conversions. Adds execute() , search() , and describe() methods to the @cloudflare/codemode durable runtime handle, enabling MCP servers and non-AI-SDK hosts to invoke Code Mode directly. Introduces Devin Outposts: run Devin agent sessions on Cloudflare-managed, container-isolated infrastructure via the Sandbox SDK. Deploys new WAF rules covering Next.js DoS (CVE-2026-64641), Next.js SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. SQL injection SQL injection An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does.
+2 more
show less
Enhances WAF generic protections against SSRF, Local File Inclusion (LFI), and Cross-Site Scripting (XSS XSS Cross-site scripting, an attack that runs malicious script in another user's browser through a trusted site. It can steal data or perform actions using the user's session. Introduces the Permission Groups API as the replacement for the deprecated Account Roles API, supporting API Token authorization and a new meta object with label and scopes in the response schema.
7 details in Everything
└──▷ BREAKING ON UPGRADE
! The Account Roles API is deprecated and replaced by the Permission Groups API; integrations must obtain Permission Group IDs from the new API and use them in Account Members API policies — legacy Role IDs must be remapped.! The PermissionGroup response replaces the legacy Role top-level description and permissions object (keyed by resource type with edit/read flags) with a meta object containing label and scopes; individual permissions are no longer returned as part of the permission group.
Agents SDK reduces MCP schema conversion, adds exposure controls for MCP in Think and Code Mode SDK adds direct host APIs
Jul 22, 2026
· release notes
Cloudflare Agents SDK adds includeMcpTools config to control MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds includeMcpTools option to @cloudflare/think Think class to opt-out of automatic MCP tool exposure in Think mode Adds execute() , search() , and describe() methods to the durable Code Mode runtime handle in @cloudflare/codemode for direct host invocation
2 details in Everything
Cloudflare Realtime launches with RealtimeKit SDKs, a global SFU SFU A Selective Forwarding Unit: a media server architecture that relays incoming WebRTC streams to other participants without decoding them, reducing server CPU cost and latency in multi-party video or data pipelines. WebRTC WebRTC A browser-native, open standard for real-time peer-to-peer audio, video, and data exchange without plugins. Cyber tools use it to tunnel traffic or exfiltrate data through connections browsers treat as legitimate.
New RealtimeKit SDK suite adds high-level APIs and pre-built UI components for live video/voice (meetings, breakout rooms, recording, chat, polls, virtual backgrounds, transcription) in just a few lines of code. New Realtime SFU (Selective Forwarding Unit) provides a low-level, unopinionated WebRTC media server running on Cloudflare's global network for developers who need full control over media routing. New managed TURN service acts as a public relay for WebRTC traffic, ensuring connectivity for users behind restrictive firewalls or NATs, with Anycast routing to the nearest Cloudflare location. TURN service supports multiple protocol options (UDP UDP A network protocol that sends individual messages without guaranteeing delivery or order. Applications trade built-in reliability for less overhead and can add their own recovery. TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it.
4 details in Everything
Cloudflare adds WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ HOW TO FIND IT
Monitor SQLite storage growth or validate data cleanup for a Durable Object namespace directly in the dashboard.
📍 In the Cloudflare dashboard, go to Workers & Pages › Durable Objects › [your SQLite-backed namespace] › Metrics and analytics, then view the Total storage chart.
New WAF rules target Adobe ColdFusion path traversal vulnerabilities (CVE-2026-48276, CVE-2026-48282) blocking unauthenticated file upload and filesystem access attacks. New WAF rules cover WordPress SQL injection SQL injection An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does. remote code execution remote code execution Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives. New emergency detection rules deployed for Generic Rules - Unauthenticated RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives. Upcoming WAF rule updates (scheduled 2026-07-27) include improved SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. Cloudflare Access now delivers the standard browser-based login flow for plaintext HTTP private applications on port 80, replacing the Cloudflare One Client notification/pop-up flow.
+1 more
show less
New Total storage chart in the Cloudflare dashboard lets you monitor SQLite storage used by a Durable Object namespace over time, showing maximum storage per hour.
6 details in Everything
Cloudflare API gains broad CloudForce One threat-intel endpoints, Magic Connector interrupts, and AI Audit robots.txt controls
└──▷ TRY IT
Aggregate CloudForce One threat events by a specific column (e.g., threat actor) to surface trending indicators across a time window.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/accounts/<account_id>/cloudforce-one/events/aggregate' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' Retrieve your zone's AI-crawler robots.txt rules in bulk to audit which AI bots are allowed or blocked across all paths.
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/zones/<zone_id>/ai-audit/robots/bulk' \
-H 'Authorization: Bearer <API_TOKEN>' Save a reusable CloudForce One event query so analysts can replay complex threat-hunt filters without rebuilding them each session.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/<account_id>/cloudforce-one/events/queries/create' \
-H 'Authorization: Bearer <API_TOKEN>' \
-H 'Content-Type: application/json' \
-d '{"name": "APT-ransomware-Q3", "query": {"filters": {"threat_type": "ransomware"}}}'
Adds Magic Connector Interrupts API: list and create interrupt events per connector (/accounts/{account_id}/magic/connectors/{connector_id}/interrupts). Adds bulk DOS event creation with relationships and indicators via CloudForce One (/accounts/{account_id}/cloudforce-one/events/create/bulk/relationships). Adds CloudForce One event aggregation by single or multiple columns with optional date filtering (/accounts/{account_id}/cloudforce-one/events/aggregate). Adds GraphQL endpoint for CloudForce One event aggregation (/accounts/{account_id}/cloudforce-one/events/graphql). Adds graph neighborhood query against R2 Data Catalog for CloudForce One events (/accounts/{account_id}/cloudforce-one/events/graph).
+8 more
show less
Adds saved event query management (list, create, read, update, delete) for CloudForce One (/accounts/{account_id}/cloudforce-one/events/queries). Adds event relationship filtering — list events related to a specific event (/accounts/{account_id}/cloudforce-one/events/{event_id}/relationships). Adds cross-dataset indicator listing and aggregation endpoints for CloudForce One intelligence (/accounts/{account_id}/cloudforce-one/events/indicators). Adds indicator type listing across multiple datasets (/accounts/{account_id}/cloudforce-one/events/indicator-types). Adds per-dataset indicator CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. /accounts/{account_id}/cloudforce-one/events/dataset/{dataset_id}/indicators). Adds full tag and tag-category management (list, create, update, delete) as source-of-truth for CloudForce One events. Adds target industry listing per dataset and from global catalog for CloudForce One threat intelligence. Adds AI Audit robots.txt API: get and bulk-get robots.txt rules per zone (/zones/{zone_id}/ai-audit/robots).
13 details in Everything
Cloudflare adds browser-based login for plaintext HTTP private apps and SQLite storage tracking for Durable Objects.
└──▷ HOW TO FIND IT
View cumulative SQLite storage consumption for a Durable Object namespace to monitor growth trends and plan capacity.
📍 In the Cloudflare dashboard, go to Workers & Pages › Durable Objects › select your namespace › Storage, then view the Total SQLite Storage chart over time.
Enables browser-based Access login flow for plaintext HTTP private applications, matching the existing HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate. Adds total SQLite storage usage tracking over time for Durable Object namespaces in the Cloudflare dashboard. New WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
3 details in Everything
Cloudflare adds browser-based login for plaintext HTTP private apps and SQLite storage tracking for Durable Objects
└──▷ HOW TO FIND IT
Monitor SQLite storage growth for a Durable Object namespace over time to plan capacity and catch runaway writes.
📍 In the Cloudflare dashboard, go to Workers & Pages › Durable Objects › select your namespace › Storage, then view the total SQLite storage usage chart.
Enables in-browser Access login flow for plaintext HTTP private applications, matching the experience already available for HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate. Adds total SQLite storage usage tracking over time for Durable Object namespaces in the Cloudflare dashboard.
2 details in Everything
WAF - WAF Release - 2026-07-21 (2026-07-21)
Jul 21, 2026
·
issue 021
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. XSS XSS Cross-site scripting, an attack that runs malicious script in another user's browser through a trusted site. It can steal data or perform actions using the user's session. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives.
Adds two new SSRF detection rules blocking restricted-protocol and obfuscated-host request forgery attempts. Adds a new LFI path traversal detection rule to the Cloudflare Managed Ruleset. Adds three new XSS rules targeting JavaScript bracket-concatenation obfuscation across body, headers, and URI. Adds targeted blocking rules for Adobe ColdFusion file-upload path traversal (CVE-2026-48276) and directory-sequence path traversal (CVE-2026-48282). Adds blocking rules for WordPress unauthenticated SQL injection SQL injection An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does.
+2 more
show less
Adds blocking rules for WordPress remote code execution remote code execution Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives. Deploys new emergency detection rules for Generic Rules - Unauthenticated RCE, Generic Rules - Auth Bypass - 2, and Generic Rules - Information Disclosure.
7 details in Everything
WAF - WAF Release - Scheduled changes for 2026-07-27 (2026-07-21)
Jul 21, 2026
·
issue 021
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. command injection command injection An attack that makes an application execute operating-system commands supplied through untrusted input. It often happens when input is passed unsafely to a shell.
New detection rule for Command Injection - Obfuscation (rule ID ...761e7a4c), deploying in Log mode on 2026-07-27. New detection rule for Generic Rules - DoS (rule ID ...90dcdb0a), deploying in Log mode on 2026-07-27. Improved SSRF - Cloud - Beta detection rule (rule ID ...c2e84e2d), deploying in Log mode on 2026-07-27.
3 details in Everything
Cloudflare One Client for Windows (version 2026.6.880.0)
Jul 21, 2026
· release notes
Cloudflare One Client for Windows reaches GA with stabilized DNS-over-TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it.
Changes DNS fallback logic to send queries over UDP UDP A network protocol that sends individual messages without guaranteeing delivery or order. Applications trade built-in reliability for less overhead and can add their own recovery.
1 detail in Everything
Run Devin on Cloudflare using Devin Outposts
Jul 21, 2026
· release notes
Devin agents can now run in isolated Cloudflare Containers via Devin Outposts
Adds Devin Outposts integration to run Devin agents on Cloudflare managed infrastructure Each Devin session now runs in an isolated sandbox backed by Cloudflare Containers
2 details in Everything
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. XSS XSS Cross-site scripting, an attack that runs malicious script in another user's browser through a trusted site. It can steal data or perform actions using the user's session.
Adds SSRF - Restricted Protocol and SSRF - Obfuscated Host detections to the Cloudflare Managed Ruleset (previously Log, now Block) Adds LFI - Path Traversal detection to the Cloudflare Managed Ruleset (previously Log, now Block) Adds XSS — JS Bracket Concat Obfuscation detections (Body, Headers, URI) to the Cloudflare Managed Ruleset
3 details in Everything
└──▷ BREAKING ON UPGRADE
! Removes Generic Rules - Command Execution - Body - Beta, Generic Rules - Command Execution - Header - Beta, and Generic Rules - Command Execution - URI - Beta detections from the Cloudflare Managed Ruleset
Faster and more secure TLS handshakes to your origins, automatically
Jul 21, 2026
· release notes
Cloudflare now automatically negotiates TLS 1.3 key exchanges with origins, preferring post-quantum post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA.
Budget alerts now on by default for Pay-as-you-go accounts
Jul 20, 2026
· release notes
Cloudflare now enables default $10 budget alerts for eligible Pay-as-you-go accounts to notify users of cumulative usage-based spend.
View total SQLite storage for Durable Object namespaces
Jul 20, 2026
· release notes
Cloudflare adds a Total storage chart in the Durable Objects dashboard to monitor per-namespace SQLite usage.
Browser-based login for plaintext HTTP private applications
Jul 20, 2026
· release notes
Cloudflare Access adds browser-based login for plaintext HTTP private apps on port 80
Adds standard browser-based login flow for HTTP private applications served over plaintext on port 80 Returns a standard Access application token via the browser instead of a client-side authentication pop-up
2 details in Everything
Cloudflare adds Privacy Pass support, letting users prove claims without revealing identity or enabling cross-request tracking.
Supports Privacy Pass tokens, enabling users to prove claims (e.g., human verification) without exposing identity or being tracked across requests.
1 detail in Everything
Cloudflare adds email preview in Activity log, browser RDP RDP A Microsoft protocol that lets a user view and control a remote Windows desktop over a network, giving cyber tools a standard channel to audit, attack-simulate, or monitor Windows systems remotely.
└──▷ HOW TO FIND IT
Inspect the full content of a sent email — HTML body, headers, and attachments — to debug deliverability issues.
📍 In the Cloudflare dashboard, go to Email › Activity log, select a sent message, and choose HTML, Text, Headers, Attachments, or Raw source tabs to inspect its content.
Adds HTML, text, headers, attachments, and raw-source preview of sent emails directly in the Email Service Activity log. Enables bulk printing of multiple PDF files as a single print job from browser-based RDP sessions. New wrangler flagship CLI commands let you create Flagship apps, bind them to Workers, switch feature flags, and run rollouts from the command line. Cloudflare Internal DNS is now generally available, consolidating public and private DNS onto a single global control plane.
4 details in Everything
Cloudflare WAF protects WordPress applications from two high-severity vulnerabilities (2026-07-17)
Jul 17, 2026
·
issue 019
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives. SQL injection SQL injection An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does.
└──▷ HOW TO FIND IT
Verify Managed Rules are enabled on a Pro/Business/Enterprise zone so the new WordPress rules are active with the Block action rather than Log.
📍 In the Cloudflare dashboard, go to Security › WAF › Managed Rules, confirm the Cloudflare Managed Ruleset is enabled, then check Security Events and filter by the two new rule IDs to monitor matching traffic while you patch WordPress.
New WAF managed rule detects and blocks SQL injection attempts targeting WordPress 6.8+ (CVE-2026-60137) before crafted parameter values reach the application. New WAF managed rule detects and blocks unauthenticated RCE attempts via the WordPress REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Both rules are automatically active for free-plan customers via the Free Ruleset and deployed with the default Block action for Pro, Business, and Enterprise Managed Ruleset customers.
3 details in Everything
WAF - WAF Release - 2026-07-17 - Emergency (2026-07-17)
Jul 17, 2026
·
issue 019
Emergency WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives. SQLi SQLi An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does.
New detection rule (7dfb2bd4708d4b88b9911dc0550664b6) added to Cloudflare Managed Ruleset to block unauthenticated RCE via malicious path sequences at Block action. New detection rule (1c060d3a371549219ee290d7ed933fcc) added to Cloudflare Managed Ruleset to block SQLi via unsanitized request parameters at Block action. New detection rule (ebd3f2df15c74ddcbf6220c9b5ec246a) added to Cloudflare Free Ruleset to block unauthenticated RCE at Block action. New detection rule (db003b39b7774859a8d588ce33697a1a) added to Cloudflare Free Ruleset to block SQLi at Block action.
4 details in Everything
Distributor, MSSP, and Agency partners can manage Organization members directly
Jul 17, 2026
· release notes
Self-serve member management for Distributor, MSSP MSSP A Managed Security Service Provider: a third-party company that operates cyber tooling and monitoring on behalf of clients, letting organizations outsource detection, response, and compliance functions.
Enables self-service addition of Organization members for Distributor, MSSP, and Agency partner organizations via the dashboard Organization > Members > Add member flow. Removes the requirement for Cloudflare-assisted manual requests or closed beta enrollment when adding members to these partner organizations. Adds Organizations dashboard access for Agency partners while retaining their existing Tenant management dashboard.
3 details in Everything
Restart, reboot, or shut down a Cloudflare One Appliance from the dashboard
Jul 17, 2026
· release notes
New API and dashboard controls to restart, reboot, or shut down a Cloudflare One Appliance
Adds POST /accounts/{account_id}/magic/connectors/{connector_id}/interrupts endpoint to trigger appliance operations via API
1 detail in Everything
New header control options for Gateway HTTP policies
Jul 17, 2026
· release notes
Cloudflare Gateway HTTP Allow policies now support add, overwrite, and delete header operations with dynamic variables
Adds add_headers field to rule_settings API for appending headers in Gateway Allow policies Adds set_headers field to rule_settings API for replacing or creating headers in Gateway Allow policies Adds delete_headers field to rule_settings API for removing headers in Gateway Allow policies Enables dynamic variable resolution using @{...} syntax in header values (e.g., @{identity.email}, @{source.ip})
4 details in Everything
Bulk print PDFs for browser-based RDP
Jul 16, 2026
· release notes
Adds Bulk Print capability for browser-based RDP RDP A Microsoft protocol that lets a user view and control a remote Windows desktop over a network, giving cyber tools a standard channel to audit, attack-simulate, or monitor Windows systems remotely.
Enables printing multiple PDF files from a clipboard panel as a single job in Cloudflare One browser-based RDP Supports bulk print in Chromium-based browsers and Firefox
2 details in Everything
Bot management fields and ASN support in Cache Rules
Jul 16, 2026
· release notes
Adds bot management fields and ASN ASN Autonomous System Number — a globally unique identifier assigned by regional internet registries to a network operator, letting routing protocols distinguish which organization controls a block of IP addresses.
cf.bot_management.score field added to Cache Rules expression filterscf.bot_management.ja3_hash field added to Cache Rules expression filterscf.bot_management.ja4 field added to Cache Rules expression filterscf.bot_management.verified_bot field added to Cache Rules expression filterscf.bot_management.static_resource field added to Cache Rules expression filters
+6 more
show less
cf.bot_management.js_detection.passed field added to Cache Rules expression filterscf.bot_management.detection_ids field added to Cache Rules expression filterscf.bot_management.tags field added to Cache Rules expression filterscf.bot_management.signed_agent field added to Cache Rules expression filterscf.bot_management.corporate_proxy field added to Cache Rules expression filtersip.src.asnum field added to Cache Rules expression filters
11 details in Everything
Manage Flagship from the command line with Wrangler
Jul 16, 2026
· release notes
Wrangler adds wrangler flagship commands to manage apps and feature flags from the terminal
Adds wrangler flagship apps create with --binding and --update-config flags to provision Flagship applications via CLI Adds wrangler flagship flags create to define boolean, string, number, or JSON feature flags for an app Adds wrangler flagship flags update, enable, and disable commands to control flag states as kill switches Adds wrangler flagship flags rollout, split, and rules update commands for traffic distribution without redeploying Workers
4 details in Everything
Internal DNS is now generally available
Jul 15, 2026
· release notes
Cloudflare Gateway Internal DNS is generally available, allowing Enterprise customers to manage private authoritative and recursive DNS views alongside public DNS.
Internal DNS enables consolidated public and private DNS operations on a single platform with unified API access and audit trails.
1 detail in Everything
Subscribe to Email Sending events with Queues
Jul 15, 2026
· release notes
Cloudflare adds Queues event subscription for Email Sending lifecycle events
Adds new Queues event subscriptions scoped to a sending domain for Email Sending events Publishes six new email delivery event types: message.delivered, message.deferred, message.bounced, message.failed, message.rejected, and message.complained
2 details in Everything
A broken DNSSEC rollover took down .al. Now 1.1.1.1 tells you when validation is bypassed (2026-07-14)
Jul 14, 2026
·
issue 017
Returns EDE 9 (DNSKEY Missing) alongside EDE 33 to expose the underlying DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit. Emits EDE 33 on every response under an active NTA — including non-DNSSEC domains — so the entire affected zone is transparently flagged.
A broken DNSSEC rollover took down .AL. Now 1.1.1.1 tells you when validation is bypassed (2026-07-14)
Jul 14, 2026
·
issue 015
1.1.1.1 now emits EDE 33 (Negative Trust Anchor) on responses served under an NTA, making DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit.
└──▷ TRY IT
Detect whether a response from 1.1.1.1 was served under a Negative Trust Anchor — useful in monitoring scripts or incident triage when a TLD TLD The rightmost label in a domain name (e.g., .com, .gov, .uk), maintained by IANA's root zone. Cyber tools filter or pivot on TLDs to scope scans, flag suspicious registrations, or classify traffic by geography or type.
copy
$ kdig @1.1.1.1 google.al
Adds EDE code 33 (Negative Trust Anchor) to all responses served while an NTA is active, signalling that DNSSEC validation was bypassed rather than silently returning an unverified answer. Surfaces EDE 9 (DNSKEY Missing) alongside EDE 33 during NTA incidents, giving operators and monitoring tools full visibility into both the underlying DNSSEC failure and the resolver's mitigation.
2 details in Everything
A broken DNSSEC rollover took down .AL. Now 1.1.1.1 tells you when validation is bypassed (2026-07-14)
Jul 14, 2026
·
issue 003
1.1.1.1 now emits EDE 33 (Negative Trust Anchor) on responses served under an NTA, making DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit.
└──▷ TRY IT
Detect whether a response from 1.1.1.1 was served under a Negative Trust Anchor — useful in monitoring scripts or incident triage when a TLD TLD The rightmost label in a domain name (e.g., .com, .gov, .uk), maintained by IANA's root zone. Cyber tools filter or pivot on TLDs to scope scans, flag suspicious registrations, or classify traffic by geography or type.
copy
$ kdig @1.1.1.1 google.al
Adds EDE code 33 (Negative Trust Anchor) to all responses served while an NTA is active, signalling that DNSSEC validation was bypassed rather than silently returning an unverified answer. Surfaces EDE 9 (DNSKEY Missing) alongside EDE 33 during NTA incidents, giving operators and monitoring tools full visibility into both the underlying DNSSEC failure and the resolver's mitigation.
2 details in Everything
A broken DNSSEC rollover took down .AL. Now 1.1.1.1 tells you when validation is bypassed (2026-07-14)
Jul 14, 2026
·
issue 002
1.1.1.1 now emits EDE 33 (Negative Trust Anchor) on responses served under an NTA, making DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit.
└──▷ TRY IT
Detect whether a response from 1.1.1.1 was served under a Negative Trust Anchor — useful in monitoring scripts or incident triage when a TLD TLD The rightmost label in a domain name (e.g., .com, .gov, .uk), maintained by IANA's root zone. Cyber tools filter or pivot on TLDs to scope scans, flag suspicious registrations, or classify traffic by geography or type.
copy
$ kdig @1.1.1.1 google.al
Adds EDE code 33 (Negative Trust Anchor) to all responses served while an NTA is active, signalling that DNSSEC validation was bypassed rather than silently returning an unverified answer. Surfaces EDE 9 (DNSKEY Missing) alongside EDE 33 during NTA incidents, giving operators and monitoring tools full visibility into both the underlying DNSSEC failure and the resolver's mitigation.
2 details in Everything
WAF - WAF Release - 2026-07-14 (2026-07-14)
Jul 14, 2026
·
issue 015
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives.
New managed rule blocks unauthenticated memory disclosure (CVE-2026-8451) targeting Citrix NetScaler ADC and Gateway appliances configured as SAML SAML A standard for passing signed identity assertions between a sign-in provider and an application. It lets a user sign in through their organization's identity provider. New managed rule blocks unauthenticated remote code execution remote code execution Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives. OS command injection OS command injection An attack that makes an application execute operating-system commands supplied through untrusted input. It often happens when input is passed unsafely to a shell.
2 details in Everything
WAF - WAF Release - Scheduled changes for 2026-07-20 (2026-07-14)
Jul 14, 2026
·
issue 015
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. XSS XSS Cross-site scripting, an attack that runs malicious script in another user's browser through a trusted site. It can steal data or perform actions using the user's session.
New detection: SSRF - Restricted Protocol (rule 7fbdc9407bdb4a4eae2b3d91215e7d31), deploying in Log mode on 2026-07-20. New detection: SSRF - Obfuscated Host (rule 6ca512d240d848d6a0c7ef42a935ee5d), deploying in Log mode on 2026-07-20. New detection: LFI - Path Traversal (rule a3fb0870c38440d8a9a0eba81b0230ac), deploying in Log mode on 2026-07-20. New detection: Adobe ColdFusion File Upload Path Traversal (CVE-2026-48276, rule 452a04be3f73458c863d8dae61349c8b), deploying in Log mode on 2026-07-20. New detection: Adobe ColdFusion Path Traversal (CVE-2026-48282, rule a53a3fb491c64d74908081ee9cb61eac), deploying in Log mode on 2026-07-20.
+1 more
show less
New detections for XSS via JavaScript bracket-concatenation obfuscation across three inspection surfaces: request body (rule d8b63828c2344d919b94d2594ac5e21f), headers (rule 264a83a764be428ca41d516ff31f5559), and URI (rule 4ba21a60837244029183b782987984fd), all deploying in Log mode on 2026-07-20.
6 details in Everything
WAF - WAF Release - Scheduled changes for 2026-07-20 (2026-07-14)
Jul 14, 2026
·
issue 003
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. XSS XSS Cross-site scripting, an attack that runs malicious script in another user's browser through a trusted site. It can steal data or perform actions using the user's session.
New detection: SSRF - Restricted Protocol (rule 7fbdc9407bdb4a4eae2b3d91215e7d31), deploying in Log mode on 2026-07-20. New detection: SSRF - Obfuscated Host (rule 6ca512d240d848d6a0c7ef42a935ee5d), deploying in Log mode on 2026-07-20. New detection: LFI - Path Traversal (rule a3fb0870c38440d8a9a0eba81b0230ac), deploying in Log mode on 2026-07-20. New detection: Adobe ColdFusion File Upload Path Traversal (CVE-2026-48276, rule 452a04be3f73458c863d8dae61349c8b), deploying in Log mode on 2026-07-20. New detection: Adobe ColdFusion Path Traversal (CVE-2026-48282, rule a53a3fb491c64d74908081ee9cb61eac), deploying in Log mode on 2026-07-20.
+1 more
show less
New detections for XSS via JavaScript bracket-concatenation obfuscation across three inspection surfaces: request body (rule d8b63828c2344d919b94d2594ac5e21f), headers (rule 264a83a764be428ca41d516ff31f5559), and URI (rule 4ba21a60837244029183b782987984fd), all deploying in Log mode on 2026-07-20.
6 details in Everything
WAF - WAF Release - 2026-07-14 (2026-07-14)
Jul 14, 2026
·
issue 003
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives.
New managed rule blocks unauthenticated memory disclosure (CVE-2026-8451) targeting Citrix NetScaler ADC and Gateway appliances configured as SAML SAML A standard for passing signed identity assertions between a sign-in provider and an application. It lets a user sign in through their organization's identity provider. New managed rule blocks unauthenticated remote code execution remote code execution Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives. OS command injection OS command injection An attack that makes an application execute operating-system commands supplied through untrusted input. It often happens when input is passed unsafely to a shell.
2 details in Everything
WAF - WAF Release - Scheduled changes for 2026-07-20 (2026-07-14)
Jul 14, 2026
·
issue 002
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. XSS XSS Cross-site scripting, an attack that runs malicious script in another user's browser through a trusted site. It can steal data or perform actions using the user's session.
New detection: SSRF - Restricted Protocol (rule 7fbdc9407bdb4a4eae2b3d91215e7d31), deploying in Log mode on 2026-07-20. New detection: SSRF - Obfuscated Host (rule 6ca512d240d848d6a0c7ef42a935ee5d), deploying in Log mode on 2026-07-20. New detection: LFI - Path Traversal (rule a3fb0870c38440d8a9a0eba81b0230ac), deploying in Log mode on 2026-07-20. New detection: Adobe ColdFusion File Upload Path Traversal (CVE-2026-48276, rule 452a04be3f73458c863d8dae61349c8b), deploying in Log mode on 2026-07-20. New detection: Adobe ColdFusion Path Traversal (CVE-2026-48282, rule a53a3fb491c64d74908081ee9cb61eac), deploying in Log mode on 2026-07-20.
+1 more
show less
New detections for XSS via JavaScript bracket-concatenation obfuscation across three inspection surfaces: request body (rule d8b63828c2344d919b94d2594ac5e21f), headers (rule 264a83a764be428ca41d516ff31f5559), and URI (rule 4ba21a60837244029183b782987984fd), all deploying in Log mode on 2026-07-20.
6 details in Everything
WAF - WAF Release - 2026-07-14 (2026-07-14)
Jul 14, 2026
·
issue 002
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives.
New managed rule blocks unauthenticated memory disclosure (CVE-2026-8451) targeting Citrix NetScaler ADC and Gateway appliances configured as SAML SAML A standard for passing signed identity assertions between a sign-in provider and an application. It lets a user sign in through their organization's identity provider. New managed rule blocks unauthenticated remote code execution remote code execution Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives. OS command injection OS command injection An attack that makes an application execute operating-system commands supplied through untrusted input. It often happens when input is passed unsafely to a shell.
2 details in Everything
Platforms can now create Temporary Accounts via the Cloudflare API
Jul 14, 2026
· release notes
New Temporary Accounts API allows platforms to create preview accounts without user login
Adds POST /client/v4/provisioning/previews/challenge endpoint to request a proof-of-work challenge for temporary account creation. Adds POST /client/v4/provisioning/previews endpoint to create a temporary preview account using the challenge solution and accepted terms. Enables deployment of Workers and supported resources to temporary accounts via returned account ID and API token, with a claim URL for permanence.
3 details in Everything
Introducing Precursor: detecting agentic behavior with continuous client-side signals (2026-07-13)
Jul 13, 2026
·
issue 015
Cloudflare launches Precursor: continuous client-side behavioral signals that extend bot detection across entire user sessions.
└──▷ HOW TO FIND IT
Enable Precursor on a zone to start collecting continuous session-level behavioral signals and feeding them into your existing bot defenses.
📍 In the Cloudflare dashboard, go to your zone › Security › Bots, find the Precursor section, toggle Precursor on, and select a verification mode (low-friction background observation or enforced Challenge for unverified sessions).
After enabling Precursor, investigate sessions showing signs of sustained automation — especially behavior occurring between individual requests.
📍 In the Cloudflare dashboard, go to Security › Security Analytics, then switch to the session-based view to filter bot management traffic by session-level signals and identify divergent visitor journeys.
Introduces Precursor, a session-based client-side verification system that dynamically injects JavaScript into HTML responses to continuously collect behavioral signals (pointer movement, keyboard timing/rhythm, focus changes, visibility) across the full user journey — no application changes required. Adds session-scoped behavioral evaluation that accumulates signal throughout a session, preventing bots from resetting their behavioral signature via page refresh or new challenge. Detects automation patterns (linear mouse interpolation, inhuman click precision, missing physiological tremor, atypical timing) by cross-referencing multiple interaction streams in an edge-side evaluation layer with a roster of modular evaluators. Feeds session-level behavioral signals directly into existing bot score, challenge decisions, and security rules — improving detection precision without adding friction for legitimate users. Introduces session-based views in Security Analytics, enabling practitioners to analyze full visitor journeys, identify where sessions diverge from expected human behavior, and surface sessions showing sustained signs of automation.
+1 more
show less
Privacy-preserving by design: keyboard activity is captured as timing and rhythm only (not keystrokes), signals are evaluated as aggregate patterns, and behavioral data is not exposed to customer dashboards or tied to user identities.
6 details in Everything
Introducing Precursor: detecting agentic behavior with continuous client-side signals (2026-07-13)
Jul 13, 2026
·
issue 003
Cloudflare launches Precursor: continuous client-side behavioral signals that extend bot detection across entire user sessions.
└──▷ HOW TO FIND IT
Enable Precursor on a zone to start collecting continuous session-level behavioral signals and feeding them into your existing bot defenses.
📍 In the Cloudflare dashboard, go to your zone › Security › Bots, find the Precursor section, toggle Precursor on, and select a verification mode (low-friction background observation or enforced Challenge for unverified sessions).
After enabling Precursor, investigate sessions showing signs of sustained automation — especially behavior occurring between individual requests.
📍 In the Cloudflare dashboard, go to Security › Security Analytics, then switch to the session-based view to filter bot management traffic by session-level signals and identify divergent visitor journeys.
Introduces Precursor, a session-based client-side verification system that dynamically injects JavaScript into HTML responses to continuously collect behavioral signals (pointer movement, keyboard timing/rhythm, focus changes, visibility) across the full user journey — no application changes required. Adds session-scoped behavioral evaluation that accumulates signal throughout a session, preventing bots from resetting their behavioral signature via page refresh or new challenge. Detects automation patterns (linear mouse interpolation, inhuman click precision, missing physiological tremor, atypical timing) by cross-referencing multiple interaction streams in an edge-side evaluation layer with a roster of modular evaluators. Feeds session-level behavioral signals directly into existing bot score, challenge decisions, and security rules — improving detection precision without adding friction for legitimate users. Introduces session-based views in Security Analytics, enabling practitioners to analyze full visitor journeys, identify where sessions diverge from expected human behavior, and surface sessions showing sustained signs of automation.
+1 more
show less
Privacy-preserving by design: keyboard activity is captured as timing and rhythm only (not keystrokes), signals are evaluated as aggregate patterns, and behavioral data is not exposed to customer dashboards or tied to user identities.
6 details in Everything
Introducing Precursor: detecting agentic behavior with continuous client-side signals (2026-07-13)
Jul 13, 2026
·
issue 002
Cloudflare launches Precursor: continuous client-side behavioral signals that extend bot detection across entire user sessions.
└──▷ HOW TO FIND IT
Enable Precursor on a zone to start collecting continuous session-level behavioral signals and feeding them into your existing bot defenses.
📍 In the Cloudflare dashboard, go to your zone › Security › Bots, find the Precursor section, toggle Precursor on, and select a verification mode (low-friction background observation or enforced Challenge for unverified sessions).
After enabling Precursor, investigate sessions showing signs of sustained automation — especially behavior occurring between individual requests.
📍 In the Cloudflare dashboard, go to Security › Security Analytics, then switch to the session-based view to filter bot management traffic by session-level signals and identify divergent visitor journeys.
Introduces Precursor, a session-based client-side verification system that dynamically injects JavaScript into HTML responses to continuously collect behavioral signals (pointer movement, keyboard timing/rhythm, focus changes, visibility) across the full user journey — no application changes required. Adds session-scoped behavioral evaluation that accumulates signal throughout a session, preventing bots from resetting their behavioral signature via page refresh or new challenge. Detects automation patterns (linear mouse interpolation, inhuman click precision, missing physiological tremor, atypical timing) by cross-referencing multiple interaction streams in an edge-side evaluation layer with a roster of modular evaluators. Feeds session-level behavioral signals directly into existing bot score, challenge decisions, and security rules — improving detection precision without adding friction for legitimate users. Introduces session-based views in Security Analytics, enabling practitioners to analyze full visitor journeys, identify where sessions diverge from expected human behavior, and surface sessions showing sustained signs of automation.
+1 more
show less
Privacy-preserving by design: keyboard activity is captured as timing and rhythm only (not keystrokes), signals are evaluated as aggregate patterns, and behavioral data is not exposed to customer dashboards or tied to user identities.
6 details in Everything
Challenges - Precursor introduces session-based bot detection (2026-07-13)
Jul 13, 2026
·
issue 015
Cloudflare Precursor adds session-based JavaScript bot detection with continuous behavioral re-evaluation across user sessions.
└──▷ HOW TO FIND IT
Enable Precursor from the Cloudflare dashboard to activate session-based bot detection for your zone.
📍 In the Cloudflare dashboard, go to Security › Bots and enable Precursor, then select your preferred mode to balance security and user experience.
New Precursor client-side JavaScript engine continuously evaluates behavioral signals across a session for bot detection. Enables re-validation of challenge clearance as session behavior changes, updating bot scores with session context. Provides client-side visibility into bot signals where no previous detection existed. Integrates with existing Security Rules and supports configurable modes to balance security and user experience. Precursor can be enabled directly from the Cloudflare dashboard.
5 details in Everything
Challenges - Precursor introduces session-based bot detection (2026-07-13)
Jul 13, 2026
·
issue 003
Cloudflare Precursor adds session-based JavaScript bot detection with continuous behavioral re-evaluation across user sessions.
└──▷ HOW TO FIND IT
Enable Precursor from the Cloudflare dashboard to activate session-based bot detection for your zone.
📍 In the Cloudflare dashboard, go to Security › Bots and enable Precursor, then select your preferred mode to balance security and user experience.
New Precursor client-side JavaScript engine continuously evaluates behavioral signals across a session for bot detection. Enables re-validation of challenge clearance as session behavior changes, updating bot scores with session context. Provides client-side visibility into bot signals where no previous detection existed. Integrates with existing Security Rules and supports configurable modes to balance security and user experience. Precursor can be enabled directly from the Cloudflare dashboard.
5 details in Everything
Challenges - Precursor introduces session-based bot detection (2026-07-13)
Jul 13, 2026
·
issue 002
Cloudflare Precursor adds session-based JavaScript bot detection with continuous behavioral re-evaluation across user sessions.
└──▷ HOW TO FIND IT
Enable Precursor from the Cloudflare dashboard to activate session-based bot detection for your zone.
📍 In the Cloudflare dashboard, go to Security › Bots and enable Precursor, then select your preferred mode to balance security and user experience.
New Precursor client-side JavaScript engine continuously evaluates behavioral signals across a session for bot detection. Enables re-validation of challenge clearance as session behavior changes, updating bot scores with session context. Provides client-side visibility into bot signals where no previous detection existed. Integrates with existing Security Rules and supports configurable modes to balance security and user experience. Precursor can be enabled directly from the Cloudflare dashboard.
5 details in Everything
R2 Data Catalog now supports read-only API tokens
Jul 13, 2026
· release notes
R2 Data Catalog now accepts read-only API tokens for Iceberg query engines.
Adds support for Admin Read only tokens to R2 Data Catalog authentication Enables least-privilege access for read-only clients like R2 SQL, DuckDB, and PyIceberg
2 details in Everything
Agents can respond to MCP elicitation requests
Jul 13, 2026
· release notes
Cloudflare Agents now handle MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds this.mcp.configureElicitationHandlers() method to enable form and URL mode elicitation in MCP-connected agents Supports form mode for structured, non-sensitive data collection from users Supports url mode for requesting consent before opening out-of-band flows
3 details in Everything
Origin Content Signals for Markdown for Agents
Jul 13, 2026
· release notes
Markdown for Agents now preserves security, cache, and Content-Signal headers from the origin.
Preserves Strict-Transport-Security , Content-Security-Policy , X-Frame-Options , Set-Cookie , and CORS CORS A browser mechanism that lets a server declare which foreign origins may read its HTTP responses, enforced by the browser to block unauthorized cross-site requests from JavaScript. Access-Control-Allow-Origin ) during HTML-to-Markdown conversion. Passes through Cache-Control , Expires , and Age caching headers. Preserves the origin's Content-Signal header; adds default Content-Signal: ai-train=yes, search=yes, ai-input=yes when missing.
3 details in Everything
Precursor introduces session-based bot detection
Jul 13, 2026
· release notes
Cloudflare Precursor introduces client-side session-based bot detection with configurable dashboard modes
Introduces Precursor , a new client-side JavaScript capability for session-based bot detection that continuously evaluates behavioral signals across a session and re-validates challenge clearance as behavior changes
1 detail in Everything
DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
└──▷ USE IT
Create a new Durable Object namespace using the now-required SQLite backend instead of the legacy key-value backend.
json
copy
{
"$schema": "./node_modules/wrangler/config-schema.json",
"migrations": [
{
"tag": "v1",
"new_sqlite_classes": ["MyDurableObject"]
}
]
}
Tune DLP source code detection sensitivity in Gateway HTTP policies by setting a confidence level to reduce false positives on legitimate documentation or chat traffic.
📍 In the Cloudflare dashboard, go to Security › DLP › Profiles, open or create a Source Code predefined profile, then set the confidence level (Higher = fewer false positives, Lower = broader coverage) before applying the profile in a Gateway HTTP policy.
Improves DLP source code detection to evaluate only whole source code file uploads/downloads, reducing false positives from code embedded in chat messages, docs, or code samples. Adds a 500-character minimum threshold for DLP source code file evaluation, filtering out small fragments that lack enough context for reliable classification. Supports confidence level tuning on DLP source code profiles to balance false-positive reduction against detection coverage in Gateway HTTP policies. Enforces SQLite storage backend for all new Durable Object namespaces on accounts without an existing KV-backed namespace — new_classes migrations now fail with an explicit error. SQLite-backed Durable Objects add point-in-time recovery, enabling storage restoration to any point within the past 30 days.
5 details in Everything
Improving Smart Tiered Cache for Public Cloud Regions (2026-07-10)
Jul 10, 2026
·
issue 012
Cloudflare Smart Tiered Cache now supports cloud region hints for AWS, GCP, Azure, and Oracle Cloud anycast origins.
└──▷ HOW TO FIND IT
Set a region hint for an anycast AWS origin so Smart Tiered Cache routes through the optimal upper tier instead of hairpinning across continents.
📍 In the Cloudflare dashboard, go to Caching › Tiered Cache › Origin Configuration. Find your anycast origin IP, click the edit icon, select Set Region Hint , and choose your region (e.g., aws:us-east-1). Save to apply.
Adds cloud region hint configuration for anycast origins, letting Smart Tiered Cache select optimal upper tiers for origins on AWS, GCP, Azure, and Oracle Cloud. New Origin Configuration table in the dashboard (Caching > Tiered Cache > Origin Configuration) enables per-IP region hint assignment or bulk editing of all origin IPs at once. Supports region hint management via Cloudflare API and Terraform for infrastructure-as-code workflows. Introduces anycast origin detection using speed-of-light latency checks across multiple global checkpoint data centers. Automatically refreshes cloud provider IP range mappings every few hours and upper-tier probe data every 15 minutes, with geographic fallback for regions lacking probe data.
5 details in Everything
Improving Smart Tiered Cache for Public Cloud Regions (2026-07-10)
Jul 10, 2026
·
issue 003
Cloudflare Smart Tiered Cache now supports cloud region hints for AWS, GCP, Azure, and Oracle Cloud anycast origins.
└──▷ HOW TO FIND IT
Set a region hint for an anycast AWS origin so Smart Tiered Cache routes through the optimal upper tier instead of hairpinning across continents.
📍 In the Cloudflare dashboard, go to Caching › Tiered Cache › Origin Configuration. Find your anycast origin IP, click the edit icon, select Set Region Hint , and choose your region (e.g., aws:us-east-1). Save to apply.
Adds cloud region hint configuration for anycast origins, letting Smart Tiered Cache select optimal upper tiers for origins on AWS, GCP, Azure, and Oracle Cloud. New Origin Configuration table in the dashboard (Caching > Tiered Cache > Origin Configuration) enables per-IP region hint assignment or bulk editing of all origin IPs at once. Supports region hint management via Cloudflare API and Terraform for infrastructure-as-code workflows. Introduces anycast origin detection using speed-of-light latency checks across multiple global checkpoint data centers. Automatically refreshes cloud provider IP range mappings every few hours and upper-tier probe data every 15 minutes, with geographic fallback for regions lacking probe data.
5 details in Everything
Improving Smart Tiered Cache for Public Cloud Regions (2026-07-10)
Jul 10, 2026
·
issue 002
Cloudflare Smart Tiered Cache now supports cloud region hints for AWS, GCP, Azure, and Oracle Cloud anycast origins.
└──▷ HOW TO FIND IT
Set a region hint for an anycast AWS origin so Smart Tiered Cache routes through the optimal upper tier instead of hairpinning across continents.
📍 In the Cloudflare dashboard, go to Caching › Tiered Cache › Origin Configuration. Find your anycast origin IP, click the edit icon, select Set Region Hint , and choose your region (e.g., aws:us-east-1). Save to apply.
Adds cloud region hint configuration for anycast origins, letting Smart Tiered Cache select optimal upper tiers for origins on AWS, GCP, Azure, and Oracle Cloud. New Origin Configuration table in the dashboard (Caching > Tiered Cache > Origin Configuration) enables per-IP region hint assignment or bulk editing of all origin IPs at once. Supports region hint management via Cloudflare API and Terraform for infrastructure-as-code workflows. Introduces anycast origin detection using speed-of-light latency checks across multiple global checkpoint data centers. Automatically refreshes cloud provider IP range mappings every few hours and upper-tier probe data every 15 minutes, with geographic fallback for regions lacking probe data.
5 details in Everything
Cloudflare adds dynamic retry delays for Workflows, DNS Firewall dashboard settings, R2 SQL editor, and npm dependency telemetry for Workers.
└──▷ USE IT
Retry a Workflow step with a longer delay after rate-limit errors and a shorter delay for transient failures — without separate queue or scheduling logic.
javascript
copy
await step.do(
"sync customer",
{
retries: {
limit: 5,
delay: ({ ctx, error }) => {
if (error.message.includes("rate limit")) {
return `${ctx.attempt * 30} seconds`;
}
return "10 seconds";
},
},
},
async () => await syncCustomer()
);
Migrate a Cloudflare Tunnel private-network route from the deprecated CIDR CIDR A notation for a block of IP addresses, such as 10.0.0.0/24. The number after the slash says how many leading address bits identify the network.
copy
$ # After: create a route with the network in the request body
curl -X POST https://api.cloudflare.com/client/v4/accounts/$ACCOUNT_ID/teamnet/routes \
-H "Authorization: Bearer $CLOUDFLARE_API_TOKEN" \
-d '{"network": "172.16.0.0/16", "tunnel_id": "'$TUNNEL_ID'", "comment": "Example comment for this route."}'
# After: update or delete using route_id
curl -X PATCH https://api.cloudflare.com/client/v4/accounts/$ACCOUNT_ID/teamnet/routes/$ROUTE_ID \
-H "Authorization: Bearer $CLOUDFLARE_API_TOKEN" \
-d '{"comment": "Updated comment for this route."}'
curl -X DELETE https://api.cloudflare.com/client/v4/accounts/$ACCOUNT_ID/teamnet/routes/$ROUTE_ID \
-H "Authorization: Bearer $CLOUDFLARE_API_TOKEN"
Supports dynamic delay functions in Workflows step retries — pass a function to retries.delay to calculate adaptive wait times based on the failed attempt context and thrown error (e.g., wait longer on rate-limit errors, shorter on transient network failures). Exposes DNS Firewall cluster settings — attack mitigation, rate limiting, negative TTL TTL Time to live, a limit on how long data remains valid or how far a packet can travel. Caches use a time limit; IP packets use a hop limit. Adds a built-in R2 SQL editor in the Cloudflare dashboard for querying R2 Data Catalog tables interactively, with syntax highlighting, autocomplete, result export, and EXPLAIN output. Wrangler now collects npm package dependency metadata (name, declared version range, exact installed version) from package.json during wrangler deploy and wrangler versions upload, enabling dependency analytics and future supply chain vulnerability alerting. Breaking change (Oct 5, 2026): connections field removed from Cloudflare Tunnel and Cloudflare Mesh list/get responses — connection details must be fetched from the dedicated GET /accounts/{account_id}/cfd_tunnel/{tunnel_id}/connections or GET /accounts/{account_id}/warp_connector/{tunnel_id}/connections endpoint.
5 details in Everything
DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Source code detection now evaluates only whole file uploads/downloads, ignoring embedded code in chat messages or documentation Adds a minimum 500 character threshold for source code evaluation to filter out small fragments lacking context Adds configurable confidence levels in Gateway HTTP policies to tune match sensitivity and reduce false positives
3 details in Everything
Cloudflare adds IPsec IPsec A suite of IETF protocols that authenticate and encrypt IP packets at the network layer, giving cyber tools a standards-based way to build VPNs or secure host-to-host tunnels without modifying applications. WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output.
└──▷ TRY IT
Look up a single AI Search item by its file path without iterating through paginated results.
copy
$ curl "https://api.cloudflare.com/client/v4/accounts/<ACCOUNT_ID>/ai-search/instances/<INSTANCE_NAME>/items?key=docs/readme.md&source=builtin" -H "Authorization: Bearer <API_TOKEN>" Run a visual query against Moondream 3.1 at the edge — useful for inline content moderation or agent screenshot inspection within a single Workers request.
javascript
copy
const result = await env.AI.run("@cf/moondream/moondream3.1-9B-A2B", {
image: imageArrayBuffer,
prompt: "Does this image contain any sensitive or adult content?",
task: "query"
});
Configure a Logpush job to stream WebSocket connection-close analytics to an HTTP endpoint, enabling spike alerts on TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it.
copy
$ curl -X POST "https://api.cloudflare.com/client/v4/accounts/<ACCOUNT_ID>/logpush/jobs" \
-H "Authorization: Bearer <API_TOKEN>" \
-H "Content-Type: application/json" \
--data '{
"dataset": "websocket_analytics",
"destination_conf": "https://my-siem.example.com/ingest",
"enabled": true
}'
Adds key query parameter to the AI Search list items endpoint for exact object-key lookups without paging through results. Extends Workers AI toMarkdown (and AI Search ingestion) to support .gif and .bmp image formats. Introduces IPsec downgrade protection (beta) via the IKE_SA_INIT_FULL_TRANSCRIPT_AUTH IKEv2 IKEv2 The second version of the Internet Key Exchange protocol, standardized by the IETF, used to negotiate and authenticate IPsec tunnels. Cyber tools build on it for reliable, fast VPN session setup with built-in NAT traversal and EAP support. Adds Moondream 3.1 (@cf/moondream/moondream3.1-9B-A2B), a 9B MoE MoE A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token. vision-language model vision-language model A vision-language model that works with images and text together, such as answering questions about a picture or describing what it contains. Launches Cloudflare Drop: deploy a static site without an account, get a 1-hour live preview URL, then optionally claim it to a Cloudflare account for a permanent deployment.
+2 more
show less
New websocket_analytics Logpush dataset for Enterprise customers streams per-connection WebSocket close reasons, close sources, TLS/TCP close codes, directional byte counts, and RayIDs. Adds new fields to existing Logpush datasets: AppliedMaxTTL and UpstreamRecordTTLs to Gateway DNS; Warnings to Gateway HTTP; CacheLockWaitedMs to HTTP requests.
7 details in Everything
New DNS Firewall UX with more dashboard settings
Jul 9, 2026
· release notes
DNS Firewall dashboard now exposes attack mitigation, rate limiting, negative TTL TTL Time to live, a limit on how long data remains valid or how far a packet can travel. Caches use a time limit; IP packets use a hop limit.
Adds attack mitigation, rate limiting, negative TTL and resolver subnet cluster options to the DNS Firewall dashboard UI Adds resizable columns and show/hide column controls to the DNS Firewall cluster table
2 details in Everything
Wi-Fi signal and network performance analytics for Cloudflare One Client devices
Jul 9, 2026
· release notes
Cloudflare One Client devices now get Wi-Fi signal and network performance analytics on the Device Monitoring page
Adds a summary with Good/Fair/Poor labels for Connection, Wi-Fi signal strength, Traffic performance, and Device health on the Device Monitoring page. Enables filtering by category and adjusting time range on the Device Monitoring page to correlate metrics with user issues.
2 details in Everything
Send npm package dependency metadata with Worker uploads
Jul 9, 2026
· release notes
Wrangler now sends npm dependency metadata with Worker uploads for supply chain analytics.
wrangler deploy and wrangler versions upload now collect npm package names, declared version ranges, and exact installed versions from package.json and include them in upload metadata.Adds the dependencies_instrumentation.enabled config key (YAML or TOML) to control whether dependency metadata is sent.
2 details in Everything
Workflows now supports delay functions when retrying
Jul 9, 2026
· release notes
Cloudflare Workflows adds dynamic delay functions to step retries via the retries.delay configuration option
retries.delay accepts a function in step.do configuration to calculate adaptive retry delays based on attempt count and error contextDynamic delay functions can return duration strings, numbers, or promises resolving to durations for flexible retry logic
2 details in Everything
Cloudflare adds RDP RDP A Microsoft protocol that lets a user view and control a remote Windows desktop over a network, giving cyber tools a standard channel to audit, attack-simulate, or monitor Windows systems remotely. /accessibilityTree API, R2 Data Catalog delete warnings, and self-serve virtual appliance registration.
└──▷ TRY IT
Retrieve the semantic accessibility tree of a page for an AI agent or automation workflow — avoids raw HTML parsing and screenshot inference.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/accounts/<accountId>/browser-run/accessibilityTree' \
-H 'Authorization: Bearer <apiToken>' \
-H 'Content-Type: application/json' \
-d '{"url": "https://example.com/"}' Self-serve register a new Cloudflare One Virtual Appliance and obtain its one-time authentication key without involving the account team.
📍 In the Zero Trust dashboard, go to Networks › Connectors, select Add an appliance , choose Virtual appliance , complete registration, and copy the authentication key shown once.
Adds file transfer controls for browser-based RDP (beta): restrict upload, download, both directions, or disable entirely per Access policy — useful for BYOD BYOD Bring Your Own Device: a policy allowing employees to use personal phones, laptops, or tablets for work, creating a network of unmanaged endpoints that cyber tools must monitor or enforce policy on. Enables Browser Isolation HTTP Isolate policies on authorization proxy (PAC PAC A Proxy Auto-Configuration file, a JavaScript snippet a browser or OS fetches to decide which proxy server to route each request through, letting cyber tools intercept or redirect traffic without per-app configuration. New Browser Run /accessibilityTree endpoint delivers the browser's structured accessibility tree (roles, names, states, hierarchy) directly to AI agents and automation workflows. R2 dashboard and Wrangler now warn before deleting objects in Data Catalog-enabled buckets to prevent Iceberg metadata corruption. Self-serve registration of Cloudflare One Virtual Appliances — generate and rotate license/auth keys directly from the dashboard Connectors page without contacting the account team.
+2 more
show less
Workflows pricing adds per-step billing (500,000 steps/month included on paid plans, then $0.80 per 100,000), effective no earlier than August 10, 2026. New WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives.
7 details in Everything
Moondream 3.1 now available on Workers AI
Jul 8, 2026
· release notes
Workers AI adds Moondream 3.1 vision-language model vision-language model A vision-language model that works with images and text together, such as answering questions about a picture or describing what it contains.
Adds @cf/moondream/moondream3.1-9B-A2B model to Workers AI for frontier-level visual reasoning Enables query task to ask open-ended questions about an image with optional reasoning parameter via env.AI.run() or /ai/run REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Enables caption task to generate short, normal, or long image descriptions Enables point task to return object coordinates matching a target phrase Enables detect task to return bounding boxes for objects matching a target phrase
5 details in Everything
IP lists, IDS, and SIP rules supported in Unified Routing
Jul 8, 2026
· release notes
Unified Routing now supports IP lists, IDS IDS An intrusion detection system, monitoring traffic or host activity for suspicious behavior and producing alerts. Detection alone does not necessarily block the activity. SIP SIP Session Initiation Protocol, an IETF signaling standard for setting up and tearing down real-time voice and video calls over IP networks, giving cyber tools a structured way to intercept, fuzz, or analyze VoIP traffic.
IP lists are now supported for accounts using Unified Routing modeIDS rules are now supported for accounts using Unified Routing modeSIP rules are now supported for accounts using Unified Routing mode
3 details in Everything
Query R2 Data Catalog tables with R2 SQL from the dashboard
Jul 8, 2026
· release notes
New R2 Data Catalog query interface with built-in SQL editor in Cloudflare dashboard
Adds the Query data action in the R2 Data Catalog dashboard section to launch a built-in SQL editor for querying Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS. Introduces an interactive SQL editor with syntax highlighting and autocomplete, eliminating the need for Wrangler CLI or REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
2 details in Everything
Cloudflare Drop lets you deploy static sites without an account via drag-and-drop upload and a 1-hour temporary preview.
Enables deploying static HTML, CSS, JavaScript, images, and fonts to Cloudflare without requiring a pre-existing Cloudflare account Provides a Claim action to convert the temporary preview into a permanent deployment in an existing or new Cloudflare account Adds support for enabling Markdown content access for AI agents on deployed sites
3 details in Everything
Workers AI toMarkdown and AI Search now supports GIF and BMP image conversion
Jul 8, 2026
· release notes
Workers AI toMarkdown and AI Search now support GIF and BMP image conversion
Adds .gif and .bmp formats to the Workers AI toMarkdown Markdown conversion pipeline
1 detail in Everything
Filter AI Search list items by exact object key
Jul 8, 2026
· release notes
AI Search list items endpoint now accepts a key query parameter for exact lookups
Allows filtering results by source alongside key to disambiguate duplicate keys across multiple data sources.
1 detail in Everything
Cloudflare WAN and Magic Transit IPsec IPsec A suite of IETF protocols that authenticate and encrypt IP packets at the network layer, giving cyber tools a standards-based way to build VPNs or secure host-to-host tunnels without modifying applications. IKEv2 IKEv2 The second version of the Internet Key Exchange protocol, standardized by the IETF, used to negotiate and authenticate IPsec tunnels. Cyber tools build on it for reliable, fast VPN session setup with built-in NAT traversal and EAP support. IKE_SA_INIT_FULL_TRANSCRIPT_AUTH extension.
Introduces a per-account feature flag for the downgrade protection capability, requiring coordination with your account team to enable
1 detail in Everything
New Browser Run endpoint for accessibility trees
Jul 7, 2026
· release notes
Cloudflare Browser Run adds /accessibilityTree endpoint for semantic page structure
Browser Isolation support for authorization proxy endpoints
Jul 7, 2026
· release notes
Browser Isolation now supports HTTP Isolate policies on Gateway authorization proxy endpoints.
Applies HTTP Isolate policies to traffic routed through authorization proxy endpoints Enables identity-based Isolate policies for PAC PAC A Proxy Auto-Configuration file, a JavaScript snippet a browser or OS fetches to decide which proxy server to route each request through, letting cyber tools intercept or redirect traffic without per-app configuration.
2 details in Everything
New WebSocket Analytics Logpush dataset
Jul 7, 2026
· release notes
Cloudflare adds a new websocket_analytics Logpush dataset for per-connection WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output.
New log fields available in the websocket_analytics dataset include ConnectionCloseReason, ConnectionCloseSource, ConnectionTransportCloseCode, and RayID.
1 detail in Everything
Your Worker can now have its own cache in front of it (2026-07-06)
Jul 6, 2026
·
issue 008
Cloudflare Workers Cache adds a tiered cache in front of Workers, configured via Wrangler and standard Cache-Control headers.
└──▷ USE IT
Enable Workers Cache for a Worker so Cloudflare's cache layer handles repeat requests before your code runs, eliminating CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware.
json
copy
{
"name": "my-worker",
"main": "src/index.ts",
"compatibility_date": "2026-05-01",
"cache": {
"enabled": true
}
}
Serve a server-rendered page at cache speed for most visitors while keeping content fresh — fresh for 5 min, stale-served for up to 1 hour while background revalidation runs.
javascript
copy
return new Response(html, {
headers: {
"Content-Type": "text/html; charset=utf-8",
"Cache-Control": "public, max-age=300, stale-while-revalidate=3600",
},
});
Purge cached entries for a specific product after an inventory update, without touching any other Worker's or zone's cached content.
javascript
copy
await ctx.cache.purge({ tags: ["product:123"] });
New Workers Cache: a tiered cache that sits in front of a Worker, enabled with a single cache.enabled block in wrangler.toml, so cacheable requests never invoke Worker code or incur CPU billing. Supports stale-while-revalidate — stale responses are served instantly while the Worker re-renders in the background, so no user ever waits on a cache refresh. Supports standard Vary header for content negotiation, storing separate cache variants per distinct header combination (e.g., Accept , Accept-Language ) with no allowlist restrictions. New ctx.cache.purge() API enables Workers to programmatically purge their own cache by tag (tags: ["product:123"]), path prefix, or everything — scoped to the Worker entrypoint, not the zone. Cache follows the Worker, not the hostname — a single Worker's cache is shared across custom domains, workers.dev, service bindings, preview URLs, and Workers for Platforms tenants.
+2 more
show less
Per-entrypoint cache control: Workers for Platforms tenants each get an isolated cache; preview deployments each get their own cache partition, preventing test traffic from polluting production. Multi-tenant-safe cache keys via ctx.props allow shaping the cache key programmatically without zone-level Cache Rules or Page Rules.
7 details in Everything
Your Worker can now have its own cache in front of it (2026-07-06)
Jul 6, 2026
·
issue 002
Cloudflare Workers Cache adds a tiered cache in front of Workers, configured via Wrangler and standard Cache-Control headers.
└──▷ USE IT
Enable Workers Cache for a Worker so Cloudflare's cache layer handles repeat requests before your code runs, eliminating CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware.
json
copy
{
"name": "my-worker",
"main": "src/index.ts",
"compatibility_date": "2026-05-01",
"cache": {
"enabled": true
}
}
Serve a server-rendered page at cache speed for most visitors while keeping content fresh — fresh for 5 min, stale-served for up to 1 hour while background revalidation runs.
javascript
copy
return new Response(html, {
headers: {
"Content-Type": "text/html; charset=utf-8",
"Cache-Control": "public, max-age=300, stale-while-revalidate=3600",
},
});
Purge cached entries for a specific product after an inventory update, without touching any other Worker's or zone's cached content.
javascript
copy
await ctx.cache.purge({ tags: ["product:123"] });
New Workers Cache: a tiered cache that sits in front of a Worker, enabled with a single cache.enabled block in wrangler.toml, so cacheable requests never invoke Worker code or incur CPU billing. Supports stale-while-revalidate — stale responses are served instantly while the Worker re-renders in the background, so no user ever waits on a cache refresh. Supports standard Vary header for content negotiation, storing separate cache variants per distinct header combination (e.g., Accept , Accept-Language ) with no allowlist restrictions. New ctx.cache.purge() API enables Workers to programmatically purge their own cache by tag (tags: ["product:123"]), path prefix, or everything — scoped to the Worker entrypoint, not the zone. Cache follows the Worker, not the hostname — a single Worker's cache is shared across custom domains, workers.dev, service bindings, preview URLs, and Workers for Platforms tenants.
+2 more
show less
Per-entrypoint cache control: Workers for Platforms tenants each get an isolated cache; preview deployments each get their own cache partition, preventing test traffic from polluting production. Multi-tenant-safe cache keys via ctx.props allow shaping the cache key programmatically without zone-level Cache Rules or Page Rules.
7 details in Everything
WAF - WAF Release - Scheduled changes for 2026-07-13 (2026-07-06)
Jul 6, 2026
·
issue 014
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives.
New detection for Citrix NetScaler ADC insufficient input validation (CVE-2026-8451), rule 78826e3223b94da493a2ade876973ac4, deploying in Log mode on 2026-07-13. New detection for Progress Kemp LoadMaster remote code execution remote code execution Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives.
2 details in Everything
WAF - WAF Release - Scheduled changes for 2026-07-13 (2026-07-06)
Jul 6, 2026
·
issue 003
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives.
New detection for Citrix NetScaler ADC insufficient input validation (CVE-2026-8451), rule 78826e3223b94da493a2ade876973ac4, deploying in Log mode on 2026-07-13. New detection for Progress Kemp LoadMaster remote code execution remote code execution Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives.
2 details in Everything
WAF - WAF Release - Scheduled changes for 2026-07-13 (2026-07-06)
Jul 6, 2026
·
issue 002
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives.
New detection for Citrix NetScaler ADC insufficient input validation (CVE-2026-8451), rule 78826e3223b94da493a2ade876973ac4, deploying in Log mode on 2026-07-13. New detection for Progress Kemp LoadMaster remote code execution remote code execution Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives.
2 details in Everything
Self-serve registration of Cloudflare One Virtual Appliance in the dashboard
Jul 6, 2026
· release notes
Self-serve registration and key generation for Cloudflare One Virtual Appliance in the dashboard Connectors page
Adds Virtual appliance option on the Connectors page to register a new virtual appliance and generate its authentication key Adds Regenerate authentication key action in a virtual appliance connector's menu to rotate the key with immediate revocation of the previous one
2 details in Everything
└──▷ BREAKING ON UPGRADE
! The previous authentication key is immediately and irrevocably revoked when using Regenerate authentication key .
Declare Durable Object class lifecycle with `exports`
Jul 4, 2026
· release notes
Wrangler adds declarative exports config for Durable Object lifecycle management
Introduces the exports configuration key in Wrangler to declaratively manage Durable Object class states (created, renamed, deleted, transferred) instead of using the legacy imperative migrations array.
1 detail in Everything
└──▷ BREAKING ON UPGRADE
! exports and migrations are mutually exclusive within a single Worker; adding exports prevents use of the legacy migrations array in that same configuration.
Simpler runtime types with @cloudflare/workers-types v5
Jul 3, 2026
· release notes
@cloudflare/workers-types v5 simplifies runtime types by exposing only latest and experimental entrypoints
Adds @cloudflare/workers-types as the primary entrypoint for latest stable compatibility date types. Adds @cloudflare/workers-types/experimental entrypoint for APIs behind experimental compatibility flags. Removes dated entrypoints such as @cloudflare/workers-types/2022-11-30 and @cloudflare/workers-types/2023-03-01.
3 details in Everything
└──▷ BREAKING ON UPGRADE
! Dated entrypoints like @cloudflare/workers-types/2022-11-30 no longer exist in the package; users must use wrangler types or the new default/experimental entrypoints.
Cloudflare Mesh now supports hostname-based traffic routing for private and public hosts.
New capability: Attract traffic by hostname to a Mesh node.
1 detail in Everything
Manage AI Search sync jobs with Wrangler CLI
Jul 2, 2026
· release notes
Wrangler CLI adds wrangler ai-search jobs subcommand group for managing AI Search sync jobs.
Adds the wrangler ai-search jobs create <instance> command to trigger new asynchronous sync jobs, with --namespace/-n and --json flags for automation Adds wrangler ai-search jobs list, get, cancel, and logs subcommands for managing existing AI Search sync jobs, supporting --page, --per-page, and --force options
2 details in Everything
Work across multiple accounts with Wrangler auth profiles
Jul 2, 2026
· release notes
Wrangler now supports named auth profiles scoped to directories for multi-account workflows
└──▷ TRY IT
Run a deployment using a specific named profile without changing directories or environment variables.
copy
$ wrangler deploy --profile personal
Adds wrangler auth create <name> and wrangler auth activate <name> <dir> commands to establish directory-scoped OAuth logins Adds the --profile flag to existing CLI commands like wrangler deploy to specify an active authentication profile for single invocations
2 details in Everything
Cache multiple versions of a URL with Vary
Jul 2, 2026
· release notes
Cloudflare Cache Rules now honor origin Vary headers with normalize, passthrough, or bypass actions
Adds normalize, passthrough, and bypass actions to the Vary setting in Cloudflare Cache Rules, allowing multiple cached versions of a single URL based on request headers like Accept-Language. Adds the cf.vary property for per-request Vary control within Workers subrequests.
2 details in Everything
Updated fields across multiple Logpush datasets in Cloudflare Logs
Jul 2, 2026
· release notes
Cloudflare Logs adds new Logpush fields to Gateway DNS, HTTP, and HTTP request datasets
Adds AppliedMaxTTL and UpstreamRecordTTLs fields to the Gateway DNS Logpush dataset Adds the Warnings field to the Gateway HTTP Logpush dataset Adds the CacheLockWaitedMs field to the HTTP requests Logpush dataset
3 details in Everything
Announcing the Monetization Gateway: charge for any resource behind Cloudflare via x402 (2026-07-01)
Jul 1, 2026
·
issue 002
Cloudflare Monetization Gateway lets you charge any caller for any resource via x402 x402 A proposed HTTP payment protocol revival using status code 402, enabling machine-to-machine micropayments over HTTP so cyber tools can gate API access or resources behind automated, per-request cryptocurrency payments.
└──▷ HOW TO FIND IT
Gate a premium API route so any agent caller — with no prior account — must pay $0.01 per request before your origin is reached.
📍 In the Cloudflare dashboard, go to Monetization Gateway › Payment Rules › Create Rule. Set the route expression to http.request.uri.path matches "/api/premium/*", verb to GET/POST, price to $0.01 USD (stablecoin), then Save and Deploy.
Monetize unauthenticated traffic by converting 401 responses into 402 Payment Required — no origin code changes needed.
📍 In the Cloudflare dashboard, go to Monetization Gateway › Payment Rules › Create Rule. Enable Intercept HTTP 401 responses and set the 402 price and stablecoin asset. Callers that would have received 401 will instead receive a 402 with payment instructions.
New Cloudflare Monetization Gateway enables usage-based payment enforcement at the edge for web pages, datasets, APIs, and MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Supports the x402 open protocol (HTTP 402 Payment Required), allowing agentic callers to discover price, pay in stablecoins, and receive access in a single HTTP round-trip with no prior account or API key. Flexible payment rules API lets you gate specific REST verbs, routes (e.g., /api/premium/*), or unauthenticated callers with per-request pricing as low as fractions of a cent. Variable pricing support enables charging different amounts based on task complexity — for example, up to $2 for compute-intensive requests like image generation. Interceptor mode converts HTTP 401 Unauthorized responses from your origin into 402 Payment Required with pricing instructions, monetizing unauthenticated traffic without origin changes.
+4 more
show less
Payment verification and enforcement runs across Cloudflare's 330+ city global network, keeping x402 handshakes low-latency and shielding origins from payment verification load. Rules manageable as code via Cloudflare API and Terraform, making paid endpoints first-class infrastructure config. Sellers can accumulate stablecoins (e.g., USDC, OUSD) and redeem them for fiat currency, with peer-to-peer settlement targeting sub-second finality. Optional integration with Web Bot Auth allows combining verified agent identity with usage-based pricing in a single request.
9 details in Everything
Making AI search smarter (2026-07-01)
Jul 1, 2026
·
issue 002
Cloudflare launches AI search quality research program and Pay Per Use experiments to compensate content creators.
└──▷ HOW TO FIND IT
Express interest in the Ceramic.ai pay-per-query or You.com pay-per-content programs to start earning compensation when your content appears in AI search results.
📍 Navigate to the Cloudflare interest form linked in the blog post (blog.cloudflare.com/making-ai-search-smarter/) and submit your details to opt in to the Ceramic or You.com compensation programs.
If you operate an answer engine and want to integrate Cloudflare's freshness/traffic signals to crawl smarter and reduce redundant fetches.
📍 Contact aeo@cloudflare.com to join the crawl-quality research program as an answer engine partner.
Launches research program to share content-freshness and traffic signals with answer engines, enabling smarter crawling that skips unchanged pages and surfaces higher-quality content. Introduces Pay Per Use model (evolving from Pay Per Crawl), letting AI companies pay content owners per query or per result rather than per crawl. New partnership with Ceramic.ai enables a pay-per-query model where publishers are compensated each time their content appears in Ceramic search results. New partnership with You.com enables on-demand, per-content payments by agents for specific premium content without upfront commitment. Adds Answer Engine Optimization (AEO) reporting for participating publishers, showing top queries driving content appearances, specific snippets surfaced, average ranking position, and more.
5 details in Everything
Your site, your rules: new AI traffic options for all customers (2026-07-01)
Jul 1, 2026
·
issue 002
Cloudflare launches granular AI traffic controls for all tiers, BotBase bot directory for Enterprise, and a new content-use signal in robots.txt.
└──▷ USE IT
Express a strict content-use preference in robots.txt so crawlers know they may index and link but must not store or reproduce content beyond excerpts.
ini
copy
# robots.txt — manually authored or via Cloudflare managed robots.txt
User-agent: *
Content-Signal: search=yes,ai-train=no,use=reference
Allow: /
Allow only Search, SEO, and Ads Verification bots up to the reference content-use level — useful for a publisher that wants discoverability but no content reproduction.
📍 In the Cloudflare dashboard, go to Security › Bots › Bot Management configuration card › BotBase, filter by classification (Search, SEO, Ads Verification), then set content use level to reference and block all other classifications.
Find a specific bot's detection ID in BotBase to target it precisely in a Security rule — useful when you want to allow one verified agent while blocking the rest of its category.
📍 In the Cloudflare dashboard, go to Security › Bots › Bot Management configuration card › BotBase, search for the bot by name, copy its Detection ID, then reference that ID in a custom Security rule.
New per-category AI traffic controls — Search, Agent, and Training — available to all customers including Free tier, replacing the single Block AI Bots toggle. New default enforcement (September 15, 2026): Training and Agent crawlers blocked by default on ad-serving pages for new domains; multi-purpose crawlers (e.g., Googlebot, BingBot) subject to the most restrictive applicable rule. Introduces BotBase, a searchable database of all known bots and agents with taxonomy classification, detection IDs, and Security-rule integration — available to Enterprise Bot Management customers via the Bot Management configuration card. New content use signal (use=) extends Content Signals in robots.txt with three levels — immediate, reference, and full — letting owners express how crawlers may store and reshare content. Managed robots.txt now automatically includes use=reference alongside existing search=yes,ai-train=no Content Signals for all customers who have enabled it.
+3 more
show less
Bot Management customers gain the ability to combine content-use levels with bot classifications (Search, Agent, Training, SEO, Ads Verification, etc.) to build nuanced allow/block rules without managing individual bots. BotBase tracks content-use behavior per bot; verified bots that abuse content signals lose Verified status. Expanded bot taxonomy now classifies bots with multiple simultaneous behaviors (e.g., a crawler that is both Search and Training) rather than a single primary label.
8 details in Everything
Unmasking the crawls with Attribution Business Insights (2026-07-01)
Jul 1, 2026
·
issue 002
Cloudflare launches Attribution Business Insights dashboard for Bot Management customers to analyze AI crawler impact.
└──▷ HOW TO FIND IT
Check your site's crawl-to-referral ratio over the past 30 days to quantify how extractive a specific AI crawler is before entering a licensing conversation.
📍 In the Cloudflare dashboard, go to Security › Bots › Attribution Business Insights, set the time range to 30 days, and review the crawl-to-referral ratio column in the per-bot-operator breakdown.
New Attribution Business Insights dashboard gives Bot Management customers a dedicated analytics hub for AI crawler and bot traffic, with no manual filtering required. Adds site-wide and per-bot-operator crawl-to-referral ratio metrics, viewable across 24-hour, 7-day, and 30-day windows. Introduces updated bot taxonomy that classifies AI crawlers as Training, Search, or Agent — going beyond a generic AI Crawler label. Top bots breakdown surfaces each bot's country of origin, bandwidth consumption, and current allow/block status in a single view. Per-operator breakdown consolidates all bots owned by a single AI company, enabling data-driven content licensing and business negotiations.
5 details in Everything
Bots - More visibility into bot traffic with BotBase and Attribution Business Insights (2026-07-01)
Jul 1, 2026
·
issue 014
Enterprise Bot Management gains BotBase bot directory and Attribution Business Insights crawl-to-referral dashboard.
└──▷ HOW TO FIND IT
Use a bot's detection ID from BotBase to build a precise Security rule that blocks a specific crawler on your zone.
📍 In the Cloudflare dashboard, go to Security › Bots › BotBase, search for the target bot, copy its detection ID, then navigate to Security › WAF › Custom Rules and create a rule matching that detection ID.
Review which AI crawlers are sending referral traffic back versus just consuming your content, to inform allow/block decisions.
📍 In the Cloudflare dashboard, go to Security › Bots › Attribution Business Insights, set the time range to 30 days, and sort operators by crawl-to-referral ratio to identify high-crawl/low-referral operators.
Adds BotBase, a searchable in-dashboard directory of every bot Cloudflare tracks, classified by behavior (Search, Agent, Training, Transact, Data Collection, SEO, Ads Verification). Enables filtering live zone traffic down to a single bot within BotBase to investigate its activity and copy its detection ID for use in Security rules. Introduces Attribution Business Insights dashboard showing crawl-to-referral ratios per bot operator over 24 hours, 7 days, or 30 days, with Allowed/Blocked/Partially blocked action status. Publishes every tracked bot from BotBase to Cloudflare Radar's public bots and agents directory.
4 details in Everything
Bots - New options to manage AI traffic (2026-07-01)
Jul 1, 2026
·
issue 014
Cloudflare now lets all plans block AI crawlers by behavior — Search, Agent, or Training — independently per page type.
└──▷ HOW TO FIND IT
Opt out of the September 15, 2026 default changes before they apply to your newly onboarded domain.
📍 In the Cloudflare dashboard, go to Security › Bots › AI Traffic and manually configure each behavior preset (Search, Agent, Training) to your preferred setting before September 15, 2026.
Introduces three independently controllable AI traffic behavior categories — Search, Agent, and Training — available to all customers including Free plan. Enables per-behavior blocking policies: block on all pages, block only on ad-displaying pages, or allow — giving fine-grained control over which AI crawlers can access content. New default policy (effective September 15, 2026) automatically blocks Training and Agent crawlers on ad-displaying pages for newly onboarded domains, with opt-out available before that date. Multi-purpose crawlers combining Search and Training behaviors will be subject to Training-class blocking rules under the new defaults.
4 details in Everything
WAF - WAF Release - 2026-07-01 (2026-07-01)
Jul 1, 2026
·
issue 014
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ HOW TO FIND IT
Override the new FortiSandbox rule from Log to Block immediately if you run FortiSandbox and want active protection rather than waiting for Cloudflare's default escalation.
📍 In the Cloudflare dashboard, go to Security › WAF › Managed Rules › Cloudflare Managed Ruleset, search for rule ID 32075e19b1494117ac5915e8d84c92c9, and set the action override to Block.
Re-enable blocking of fake Bing/MSN bots via a custom WAF rule if your zone depended on rule ae20608d93b94e97988db1bbc12cf9c8 for bot enforcement.
📍 In the Cloudflare dashboard, go to Security › WAF › Custom Rules, create a new rule with field User Agent matching known fake-bot patterns, and set action to Block.
New detection for Fortinet FortiSandbox path traversal (CVE-2026-39813): rule 32075e19b1494117ac5915e8d84c92c9 blocks unauthenticated arbitrary file reads, currently set to Log action. Breaking change: Anomaly:Header:User-Agent - Fake Bing or MSN Bot rule (ae20608d93b94e97988db1bbc12cf9c8) action changed from Enabled/Block to Disabled — zones relying on this rule for bot enforcement must now implement alternative coverage.
2 details in Everything
Bots - New options to manage AI traffic (2026-07-01)
Jul 1, 2026
·
issue 003
Cloudflare now lets all plans block AI crawlers by behavior — Search, Agent, or Training — independently per page type.
└──▷ HOW TO FIND IT
Opt out of the September 15, 2026 default changes before they apply to your newly onboarded domain.
📍 In the Cloudflare dashboard, go to Security › Bots › AI Traffic and manually configure each behavior preset (Search, Agent, Training) to your preferred setting before September 15, 2026.
Introduces three independently controllable AI traffic behavior categories — Search, Agent, and Training — available to all customers including Free plan. Enables per-behavior blocking policies: block on all pages, block only on ad-displaying pages, or allow — giving fine-grained control over which AI crawlers can access content. New default policy (effective September 15, 2026) automatically blocks Training and Agent crawlers on ad-displaying pages for newly onboarded domains, with opt-out available before that date. Multi-purpose crawlers combining Search and Training behaviors will be subject to Training-class blocking rules under the new defaults.
4 details in Everything
Bots - More visibility into bot traffic with BotBase and Attribution Business Insights (2026-07-01)
Jul 1, 2026
·
issue 003
Enterprise Bot Management gains BotBase bot directory and Attribution Business Insights crawl-to-referral dashboard.
└──▷ HOW TO FIND IT
Use a bot's detection ID from BotBase to build a precise Security rule that blocks a specific crawler on your zone.
📍 In the Cloudflare dashboard, go to Security › Bots › BotBase, search for the target bot, copy its detection ID, then navigate to Security › WAF › Custom Rules and create a rule matching that detection ID.
Review which AI crawlers are sending referral traffic back versus just consuming your content, to inform allow/block decisions.
📍 In the Cloudflare dashboard, go to Security › Bots › Attribution Business Insights, set the time range to 30 days, and sort operators by crawl-to-referral ratio to identify high-crawl/low-referral operators.
Adds BotBase, a searchable in-dashboard directory of every bot Cloudflare tracks, classified by behavior (Search, Agent, Training, Transact, Data Collection, SEO, Ads Verification). Enables filtering live zone traffic down to a single bot within BotBase to investigate its activity and copy its detection ID for use in Security rules. Introduces Attribution Business Insights dashboard showing crawl-to-referral ratios per bot operator over 24 hours, 7 days, or 30 days, with Allowed/Blocked/Partially blocked action status. Publishes every tracked bot from BotBase to Cloudflare Radar's public bots and agents directory.
4 details in Everything
WAF - WAF Release - 2026-07-01 (2026-07-01)
Jul 1, 2026
·
issue 003
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ HOW TO FIND IT
Override the new FortiSandbox rule from Log to Block immediately if you run FortiSandbox and want active protection rather than waiting for Cloudflare's default escalation.
📍 In the Cloudflare dashboard, go to Security › WAF › Managed Rules › Cloudflare Managed Ruleset, search for rule ID 32075e19b1494117ac5915e8d84c92c9, and set the action override to Block.
Re-enable blocking of fake Bing/MSN bots via a custom WAF rule if your zone depended on rule ae20608d93b94e97988db1bbc12cf9c8 for bot enforcement.
📍 In the Cloudflare dashboard, go to Security › WAF › Custom Rules, create a new rule with field User Agent matching known fake-bot patterns, and set action to Block.
New detection for Fortinet FortiSandbox path traversal (CVE-2026-39813): rule 32075e19b1494117ac5915e8d84c92c9 blocks unauthenticated arbitrary file reads, currently set to Log action. Breaking change: Anomaly:Header:User-Agent - Fake Bing or MSN Bot rule (ae20608d93b94e97988db1bbc12cf9c8) action changed from Enabled/Block to Disabled — zones relying on this rule for bot enforcement must now implement alternative coverage.
2 details in Everything
WAF - WAF Release - 2026-07-01 (2026-07-01)
Jul 1, 2026
·
issue 002
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ HOW TO FIND IT
Override the new FortiSandbox rule from Log to Block immediately if you run FortiSandbox and want active protection rather than waiting for Cloudflare's default escalation.
📍 In the Cloudflare dashboard, go to Security › WAF › Managed Rules › Cloudflare Managed Ruleset, search for rule ID 32075e19b1494117ac5915e8d84c92c9, and set the action override to Block.
Re-enable blocking of fake Bing/MSN bots via a custom WAF rule if your zone depended on rule ae20608d93b94e97988db1bbc12cf9c8 for bot enforcement.
📍 In the Cloudflare dashboard, go to Security › WAF › Custom Rules, create a new rule with field User Agent matching known fake-bot patterns, and set action to Block.
New detection for Fortinet FortiSandbox path traversal (CVE-2026-39813): rule 32075e19b1494117ac5915e8d84c92c9 blocks unauthenticated arbitrary file reads, currently set to Log action. Breaking change: Anomaly:Header:User-Agent - Fake Bing or MSN Bot rule (ae20608d93b94e97988db1bbc12cf9c8) action changed from Enabled/Block to Disabled — zones relying on this rule for bot enforcement must now implement alternative coverage.
2 details in Everything
Bots - New options to manage AI traffic (2026-07-01)
Jul 1, 2026
·
issue 002
Cloudflare now lets all plans block AI crawlers by behavior — Search, Agent, or Training — independently per page type.
└──▷ HOW TO FIND IT
Opt out of the September 15, 2026 default changes before they apply to your newly onboarded domain.
📍 In the Cloudflare dashboard, go to Security › Bots › AI Traffic and manually configure each behavior preset (Search, Agent, Training) to your preferred setting before September 15, 2026.
Introduces three independently controllable AI traffic behavior categories — Search, Agent, and Training — available to all customers including Free plan. Enables per-behavior blocking policies: block on all pages, block only on ad-displaying pages, or allow — giving fine-grained control over which AI crawlers can access content. New default policy (effective September 15, 2026) automatically blocks Training and Agent crawlers on ad-displaying pages for newly onboarded domains, with opt-out available before that date. Multi-purpose crawlers combining Search and Training behaviors will be subject to Training-class blocking rules under the new defaults.
4 details in Everything
Bots - More visibility into bot traffic with BotBase and Attribution Business Insights (2026-07-01)
Jul 1, 2026
·
issue 002
Enterprise Bot Management gains BotBase bot directory and Attribution Business Insights crawl-to-referral dashboard.
└──▷ HOW TO FIND IT
Use a bot's detection ID from BotBase to build a precise Security rule that blocks a specific crawler on your zone.
📍 In the Cloudflare dashboard, go to Security › Bots › BotBase, search for the target bot, copy its detection ID, then navigate to Security › WAF › Custom Rules and create a rule matching that detection ID.
Review which AI crawlers are sending referral traffic back versus just consuming your content, to inform allow/block decisions.
📍 In the Cloudflare dashboard, go to Security › Bots › Attribution Business Insights, set the time range to 30 days, and sort operators by crawl-to-referral ratio to identify high-crawl/low-referral operators.
Adds BotBase, a searchable in-dashboard directory of every bot Cloudflare tracks, classified by behavior (Search, Agent, Training, Transact, Data Collection, SEO, Ads Verification). Enables filtering live zone traffic down to a single bot within BotBase to investigate its activity and copy its detection ID for use in Security rules. Introduces Attribution Business Insights dashboard showing crawl-to-referral ratios per bot operator over 24 hours, 7 days, or 30 days, with Allowed/Blocked/Partially blocked action status. Publishes every tracked bot from BotBase to Cloudflare Radar's public bots and agents directory.
4 details in Everything
Cloudflare introduces granular AI traffic management with Search, Agent, and Training behaviors for Bots settings.
Allows control over AI crawler behavior (Search, Agent, Training) to block or allow traffic based on intent Enables per-preset blocking choices: block on all pages, block only on pages that display ads, or do not block
2 details in Everything
More visibility into bot traffic with BotBase and Business Insights
Jul 1, 2026
· release notes
Enterprise Bot Management adds BotBase directory and Business Insights dashboard for bot visibility
Adds BotBase, a searchable directory of every known bot and agent available in the Cloudflare dashboard Adds Business Insights dashboard showing crawl-to-referral ratios per bot operator over configurable time windows Enables copying a bot's detection ID from BotBase to target it precisely in Security rules
3 details in Everything
Independent MFA for infrastructure applications
Jul 1, 2026
· release notes
Cloudflare Access for Infrastructure now supports independent MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone.
Adds YubiKey PIV key support as an MFA factor for SSH connections in Access for Infrastructure. Enables per-application and per-policy configuration of PIV authentication to enforce it for sensitive usernames like root. Allows configuration of MFA session duration to control re-authentication frequency.
3 details in Everything
Images binding is now billed per unique transformation
Jul 1, 2026
· release notes
Cloudflare Images binding now bills per unique transformation and excludes .info() calls from billing.
Adds per-unique-transformation billing for the Images binding, matching URL-based transformation pricing
1 detail in Everything
Use Google Artifact Registry images with Containers
Jul 1, 2026
· release notes
Wrangler now supports pulling container images from Google Artifact Registry via --gar-email and registry configuration.
Adds --gar-email argument to wrangler containers registries configure to specify the Google service account email. Enables use of fully qualified Google Artifact Registry image references (e.g. <REGION>-docker.pkg.dev/<PROJECT_ID>/<REPOSITORY>/<IMAGE>:<TAG>) in wrangler.toml and JSON config schemas for Containers. Supports configuring Google Artifact Registry as a container registry by piping service account JSON key through stdin to npx wrangler containers registries configure <REGION> -docker.pkg.dev.
3 details in Everything
Account-scoped firewall events dataset in Logpush
Jun 30, 2026
· release notes
Logpush now supports account-scoped firewall_events dataset with ZoneName field
Adds firewall_events as a new account-scoped dataset in Logpush, allowing a single job to capture events for all zones Adds ZoneName field to the firewall_events dataset to identify the source zone
2 details in Everything
New permissions and roles for Gateway policies and lists
Jun 30, 2026
· release notes
Cloudflare Gateway adds granular resource-scoped roles for policies and lists
Adds Zero Trust Gateway Firewall Policies Admin role to view and edit all Gateway firewall policies (DNS, HTTP, Network) Adds Zero Trust Gateway DNS Policies Admin role for specific DNS policy management Adds Zero Trust Gateway HTTP Policies Admin role for specific HTTP policy management Adds Zero Trust Gateway Network Policies Admin role for specific Network policy management Adds Zero Trust Gateway Egress Policies Admin role for specific Egress policy management
+9 more
show less
Adds Zero Trust Gateway Resolver Policies Admin role for specific Resolver policy management Adds Zero Trust Gateway Policies Admin role to view and edit all Gateway policies Adds Zero Trust Gateway Policies Read role to view all Gateway policies in read-only mode Adds Zero Trust Gateway Read Only role to view all Gateway resources Adds Zero Trust DNS Locations Admin role for DNS location management Adds Zero Trust Proxy Endpoints Admin role for Proxy Endpoint management Adds Zero Trust Account Lists Admin role for Gateway and Access list management Adds Zero Trust Account Lists Read role to view all Gateway and Access lists Enables assignment of resource-scoped roles to individual Gateway policies or Cloudflare One lists
14 details in Everything
Track memory usage for Workers and Durable Objects in the dashboard
Jun 30, 2026
· release notes
Dashboard Memory Usage metrics and GraphQL fields for Workers and Durable Objects
Adds a Memory Usage chart in the Workers Metrics tab showing P50, P90, P99, and P999 percentiles of V8 isolate memory for Workers. Adds filterable Memory Usage metrics by DO ID or name in the Durable Object namespace dashboard. Exposes workersInvocationsAdaptive GraphQL dataset with quantiles.memoryUsageBytesP50 through quantiles.memoryUsageBytesP999 fields for programmatic querying.
3 details in Everything
Cloudflare One Client for Windows (version 2026.6.822.0)
Jun 29, 2026
· release notes
Cloudflare One Client 2026.6.822.0 adds mandatory pre-auth traffic block, hardware-backed device registration, and emergency disconnect via local file signal.
Adds mandatory pre-boot authentication that blocks all Internet traffic until the user authenticates Enables hardware-backed device registration using TPM TPM A dedicated hardware chip, standardized by the Trusted Computing Group, that stores cryptographic keys and measurements in tamper-resistant silicon, giving cyber tools a root of trust that software alone cannot fake. Allows Emergency Disconnect triggers via a monitored local file in addition to HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate.
3 details in Everything
Cloudflare One Client for macOS (version 2026.6.822.0)
Jun 29, 2026
· release notes
Cloudflare One Client for macOS 2026.6.822.0 introduces GA status with hardware-backed registration, emergency disconnect file signals, and new debug CLI commands.
└──▷ USE IT
Diagnose connection issues interactively via the command line
shell
copy
warp-cli debug
Adds api.devices.cloudflare.com as the unified SNI SNI A TLS extension that lets a client declare which hostname it is connecting to during the handshake, allowing one server to host multiple certificates on a single IP address. Supports DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit. Enables hardware-backed device registration using Secure Enclave tokens Adds a new local-file signal source for Emergency Disconnect triggers Introduces warp-cli debug commands for interactive connection diagnosis
+2 more
show less
Supports ${serial_number} and ${device_uuid} template variables in Client Certificate SAN fields Adds new MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies.
7 details in Everything
└──▷ BREAKING ON UPGRADE
! API traffic now routes exclusively through api.devices.cloudflare.com; systems using SNI inspection must allow this domain as zero-trust-client.cloudflareclient.com and notifications.cloudflareclient.com are no longer used for API requests.
Cloudflare One Client for Linux (version 2026.6.822.0)
Jun 29, 2026
· release notes
Linux client v2026.6.822.0 adds hardware-backed TPM TPM A dedicated hardware chip, standardized by the Trusted Computing Group, that stores cryptographic keys and measurements in tamper-resistant silicon, giving cyber tools a root of trust that software alone cannot fake. DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit. SNI SNI A TLS extension that lets a client declare which hostname it is connecting to during the handshake, allowing one server to host multiple certificates on a single IP address.
└──▷ USE IT
Diagnose active tunnel connectivity issues directly from the Linux CLI without external tools.
shell
copy
warp-cli debug
warp-cli debug commands enable interactive connection diagnosis for the local tunnel.Emergency Disconnect triggers when a local disk file is present, allowing offline kill-switch behavior even if Cloudflare infrastructure is unreachable. DNSSEC passthrough in the local DNS proxy forwards signed responses (including DO/AD bits and RRSIG records) intact to applications validating locally. Device-profile / network policy pushes DNS search suffixes to the client, appending them to single-label queries alongside system-configured suffixes. Device registration requires TPM 2.0+ for hardware-backed token generation when available, raising the floor against device impersonation.
+2 more
show less
Path MTU Discovery (PMTUD) is now enabled by default in the client stack. API traffic for the client is unified under the api.devices.cloudflare.com SNI, deprecating the previous use of zero-trust-client.cloudflareclient.com and notifications.cloudflareclient.com for API calls.
7 details in Everything
└──▷ BREAKING ON UPGRADE
! Administrators relying on SNI inspection must update firewall rules to allow api.devices.cloudflare.com for the client, as previous versions used zero-trust-client.cloudflareclient.com and notifications.cloudflareclient.com.
Workers fetch requests now support cf.vary
Jun 28, 2026
· release notes
Workers fetch() now accepts cf.vary to control Vary header caching per subrequest
Adds cf.vary configuration option in the Cloudflare Workers fetch() call to control origin caching via the Vary header for single subrequests Supports default config with action set to bypass Supports per-header config in headers object allowing action: "normalize" with typed arrays like media_types and languages
3 details in Everything
Agents SDK adds background sub-agents and a unified turn entry point
Jun 26, 2026
· release notes
Cloudflare Agents SDK v0.17.0 adds background sub-agents via runAgentTool, unified turn entry point runTurn, and reportProgress.
Adds runAgentTool with detached: { onFinish, maxBudgetMs } to dispatch non-blocking background sub-agents Introduces runTurn({ mode }) as a unified turn admission facade supporting wait, submit, and stream modes Adds reportProgress method in sub-agents with AgentToolRunState.progress exposure via useAgentToolEvents Enables detached: { notify: true } to inject background results directly into the chat stream Introduces chatStreamStallTimeoutMs watchdog in AIChatAgent for hung transport detection
+2 more
show less
Enables repairInterruptedToolPart(part) hook override in AIChatAgent for transcript repair customization Adds connectionError/onConnectionError on AgentClient, useAgent, and useAgentChat for terminal WS failures
7 details in Everything
Service token support for MCP server portals
Jun 26, 2026
· release notes
Adds Service Token support for MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Supports Access service token authentication for MCP server portals via CF-Access-Client-Id and CF-Access-Client-Secret headers. Introduces the on_behalf: false setting to disable per-user OAuth in favor of admin credential usage.
2 details in Everything
New `us` jurisdiction for Durable Objects
Jun 26, 2026
· release notes
Cloudflare introduces us jurisdiction for Durable Objects to restrict compute and storage within the United States.
Adds a new us jurisdiction option for Durable Objects, restricting data residency to the United States.
1 detail in Everything
How we built saga rollbacks for Cloudflare Workflows (2026-06-25)
Jun 25, 2026
·
issue 001
Cloudflare Workflows adds saga rollback support: define compensation logic inline with each step.do() call.
└──▷ USE IT
Guard a credit step against partial execution — check for undefined output so the rollback handler is safe even if the step never persisted a return value.
js
copy
const credit = await step.do(
"credit-account-b",
async () => {
return await bankB.credit({
accountId: toAccountId,
amount,
idempotencyKey: `${transferId}:credit-account-b`,
});
},
{
rollback: async ({ output }) => {
if (output === undefined) {
return; // step failed before persisting — nothing to reverse
}
await bankB.debit({
accountId: toAccountId,
amount,
idempotencyKey: `${transferId}:rollback-credit-account-b`,
});
},
}
);
Adds saga rollback support to Cloudflare Workflows via a rollback option on step.do() , letting developers declare compensation logic directly alongside each step rather than in manual try/catch blocks. Rollback handlers automatically execute in reverse step-start order when a Workflow fails terminally, covering both completed and partially-executed steps. Rollback handlers receive the step's persisted output (or undefined if the step failed before persisting), enabling safe conditional compensation. Supports per-rollback retry and timeout configuration via a rollbackConfig object, mirroring the existing WorkflowStepConfig pattern. Emits lifecycle events for rollback start, individual handler failures, and rollback completion, enabling observability into compensation execution.
5 details in Everything
Test Durable Object eviction with new cloudflare:test helpers
Jun 25, 2026
· release notes
Adds evictDurableObject and evictAllDurableObjects test helpers in @cloudflare/vitest-pool-workers for Durable Object eviction testing
Adds evictDurableObject(stub) and evictDurableObject(stub, { webSockets: 'close' }) to test specific Durable Object instance eviction behavior in vitest tests Adds evictAllDurableObjects() helper to evict all running Durable Objects in evictable namespaces during testing
2 details in Everything
New name query parameter on Token API endpoints and dashboard search
/user/tokens and /accounts/{account_id}/tokens endpoints now accept a name query parameter to filter tokens by name.Dashboard UI for Account and User API tokens now includes a search bar to filter tokens by name.
2 details in Everything
Unlocking the Cloudflare app ecosystem with OAuth for all (2026-06-24)
Jun 24, 2026
·
issue 001
Cloudflare opens self-managed OAuth to all customers, enabling any developer to build scoped, delegated integrations on the Cloudflare API.
└──▷ HOW TO FIND IT
Create your first OAuth app to offer delegated Cloudflare API access to your SaaS SaaS Software delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally.
📍 In the Cloudflare dashboard, navigate to: My Profile (or Account) › OAuth Apps › Create OAuth Application, then configure your redirect URIs and desired scopes.
Enables any Cloudflare customer to create and manage their own OAuth applications for delegated API access, replacing the previously invite-only partner program. Supports standard OAuth flows with scoped consent, allowing SaaS integrations, internal developer platforms, and agentic tools to request granular permissions from users. Adds OAuth app revocation controls to the Cloudflare dashboard, giving users visibility and control over which third-party applications can access their account. Improves OAuth consent UI to clearly display which application is requesting access and exactly which permissions it will receive, reducing phishing risk. Delivers significant OAuth engine performance improvements: API P95 latency reduced ~45% (185ms → 101ms), CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware.
5 details in Everything
New WebSocket Analytics Logpush dataset and updated fields
Jun 24, 2026
· release notes
New WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output.
Adds a new WebSocket Analytics Logpush dataset with fields including BytesReceivedClient, BytesSentOrigin, ColoCode, and EdgeEndTimestamp for real-time WebSocket monitoring Extends Firewall events dataset to support account-scope Logpush via the ZoneName field, in addition to existing zone scope Adds BCC, DKIMResult , DMARCPolicy , DMARCResult , and SPFResult fields to the Email Security Alerts Logpush dataset
3 details in Everything
Cloudflare One Client for macOS (version 2026.6.782.1)
Jun 24, 2026
· release notes
Cloudflare One Client for macOS adds hardware-backed Secure Enclave device registration and default Path MTU Discovery.
Registration tokens generated in the Secure Enclave for hardware-backed device registration security. Path MTU Discovery (PMTUD) enabled by default. New client UI surfaces Split tunnel configuration and Local Domain Fallback configuration options. Ability to configure proxy mode added for consumer users.
4 details in Everything
Audit Logs v2 — Organization-level audit logs in Cloudflare dashboard
Jun 24, 2026
· release notes
Cloudflare introduces organization-level audit logs in the dashboard for Super Administrators.
Adds Organizations > Manage Organization > Audit Logs UI path for viewing organization-level audit logs Enables filtering and searching logs by actor, action, result, resource, request details, and timestamp
2 details in Everything
Control AI Search similarity cache freshness
Jun 24, 2026
· release notes
AI Search similarity cache now supports configurable TTL TTL Time to live, a limit on how long data remains valid or how far a packet can travel. Caches use a time limit; IP packets use a hop limit. cache_ttl setting and on-demand purge endpoint.
Adds cache_ttl setting (10 minutes to 6 days) to AI Search instances, defaulting to 48 hours for similarity cache freshness Adds POST /accounts/$ACCOUNT_ID/ai-search/instances/$INSTANCE_NAME/purge_cache endpoint to clear cached responses on demand
2 details in Everything
WAF - WAF Release - 2026-06-23 (2026-06-23)
Jun 23, 2026
·
issue 014
New managed rule blocks CVE-2026-10520 pre-auth OS command injection OS command injection An attack that makes an application execute operating-system commands supplied through untrusted input. It often happens when input is passed unsafely to a shell.
└──▷ HOW TO FIND IT
Verify the new Ivanti Sentry rule is active in Block mode on your zone — useful immediately after deployment to confirm coverage before patching.
📍 In the Cloudflare dashboard, go to Security › WAF › Managed Rules › Cloudflare Managed Ruleset, search for rule ID 500a90789f874345b60b0de7242fdf83, and confirm the action is set to Block.
WAF - WAF Release - 2026-06-23 (2026-06-23)
Jun 23, 2026
·
issue 003
New managed rule blocks CVE-2026-10520 pre-auth OS command injection OS command injection An attack that makes an application execute operating-system commands supplied through untrusted input. It often happens when input is passed unsafely to a shell.
└──▷ HOW TO FIND IT
Verify the new Ivanti Sentry rule is active in Block mode on your zone — useful immediately after deployment to confirm coverage before patching.
📍 In the Cloudflare dashboard, go to Security › WAF › Managed Rules › Cloudflare Managed Ruleset, search for rule ID 500a90789f874345b60b0de7242fdf83, and confirm the action is set to Block.
WAF - WAF Release - 2026-06-23 (2026-06-23)
Jun 23, 2026
·
issue 002
New managed rule blocks CVE-2026-10520 pre-auth OS command injection OS command injection An attack that makes an application execute operating-system commands supplied through untrusted input. It often happens when input is passed unsafely to a shell.
└──▷ HOW TO FIND IT
Verify the new Ivanti Sentry rule is active in Block mode on your zone — useful immediately after deployment to confirm coverage before patching.
📍 In the Cloudflare dashboard, go to Security › WAF › Managed Rules › Cloudflare Managed Ruleset, search for rule ID 500a90789f874345b60b0de7242fdf83, and confirm the action is set to Block.
Workflows rollback handlers now include step context
Jun 23, 2026
· release notes
Cloudflare Workflows rollback handlers now receive step context via ctx object
Rollback handlers can now accept a rollbackConfig parameter to control retries and timeout specifically for the rollback logic.
1 detail in Everything
Regionalized IP Bindings for Regional Services
Jun 23, 2026
· release notes
New Regionalized IP Bindings let you bind BYOIP BYOIP Bring Your Own IP — a cloud provider feature letting customers move their own publicly routable IP blocks into the provider's network, so traffic to those addresses routes through the cloud without renumbering.
Adds support for Regionalized IP Bindings to map BYOIP CIDR CIDR A notation for a block of IP addresses, such as 10.0.0.0/24. The number after the slash says how many leading address bits identify the network.
1 detail in Everything
R2 SQL now supports window functions, DISTINCT, and set operations
Jun 22, 2026
· release notes
R2 SQL adds window functions (ROW_NUMBER, RANK...), QUALIFY filtering, DISTINCT modifiers, set operations (UNION, INTERSECT, EXCEPT), and exact aggregates (MEDIAN, PERCENTILE
QUALIFY clause to filter rows based on window function resultsWindow functions: ROW_NUMBER, RANK, DENSE_RANK, PERCENT_RANK, CUME_DIST, NTILE, LAG, LEAD, FIRST_VALUE, LAST_VALUE, NTH_VALUE, and aggregates with OVER (...) including PARTITION BY and frames SELECT DISTINCT, DISTINCT ON (...), and DISTINCT modifier on aggregates like COUNT(DISTINCT ...) Grouping extensions: GROUPING SETS, ROLLUP, and CUBE Exact aggregates: MEDIAN, PERCENTILE_CONT, ARRAY_AGG, and STRING_AGG
5 details in Everything
Temporary Cloudflare Accounts for AI agents (2026-06-19)
Jun 19, 2026
·
issue 001
Cloudflare introduces Temporary Accounts for AI agents, enabling instant Worker deployments via wrangler deploy --temporary with no sign-up required.
└──▷ TRY IT
Let a background AI agent deploy a Worker immediately — no account, no token copy-pasting, no browser auth required.
copy
$ wrangler deploy --temporary Claim the temporary account to make it permanent — navigate to the claim URL printed by Wrangler and sign in or sign up to take ownership of the Worker and its bindings.
📍 In the Cloudflare dashboard, open the claim URL provided in Wrangler output, then sign in or create an account to permanently claim the temporary account and all deployed resources.
New --temporary flag in Wrangler lets AI agents deploy Cloudflare Workers instantly without a pre-existing account or authentication flow. Temporary accounts provision an API token and a claim URL automatically, giving agents a full deploy-iterate-verify loop without human intervention. Deployed Workers and associated resources (databases, bindings) stay live for 60 minutes, after which the account auto-expires unless claimed by a human. Wrangler now surfaces a prompt message about --temporary when unauthenticated, enabling agents to self-discover and adopt the flag without explicit human instruction. Agents can redeploy updated Worker scripts multiple times within the 60-minute window against the same temporary account.
5 details in Everything
Manage all your routes from one page in the dashboard
Jun 19, 2026
· release notes
Unified Routes page in Cloudflare dashboard combines Mesh, Tunnel, WAN and Magic Transit routes into a single management view
Temporary accounts for AI agent deployments
Jun 19, 2026
· release notes
Wrangler now supports deploying Workers to temporary preview accounts via the --temporary flag for unauthenticated agent workflows
Adds --temporary flag to wrangler deploy command enabling deployment without a Cloudflare account or API token Adds support for temporary preview accounts supporting Workers, Workers Static Assets, Workers KV, D1, Durable Objects, Hyperdrive, Queues, and SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination.
2 details in Everything
New Asia-Pacific location hints: apac-ne and apac-se
Jun 19, 2026
· release notes
Durable Objects gains new apac-ne and apac-se location hints for finer-grained Asia-Pacific placement
Adds apac-ne (Northeast Asia-Pacific) as a supported locationHint value for Durable Objects stub initialization Adds apac-se (Southeast Asia-Pacific) as a supported locationHint value for Durable Objects stub initialization
2 details in Everything
Cloudflare identity provider is now the default for new accounts
Jun 18, 2026
· release notes
Cloudflare Zero Trust orgs now default to Cloudflare identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. OTP OTP One-time password: a short-lived numeric or alphanumeric code valid for a single authentication attempt, generated via TOTP or HOTP standards, giving cyber tools phishing-resistant second-factor verification without stored shared secrets.
Updated Workers AI popularity metric in Cloudflare Radar
Jun 18, 2026
· release notes
Cloudflare Radar updates Workers AI popularity metric from unique accounts to inference count
Radar now measures Workers AI model and task popularity by the number of inferences rather than unique accounts. Updated metrics are accessible via /ai/inference/summary/{dimension} and /ai/inference/timeseries_groups/{dimension} API endpoints.
2 details in Everything
Cloudflare Fonts error handling and security improvements
Jun 18, 2026
· release notes
Cloudflare Fonts forwards invalid path requests to origin instead of returning 4xx/5xx errors
Cloudflare Fonts now forwards /cf-fonts requests for invalid paths or unexpected runtime errors to your origin server, replacing previous direct 4xx or 5xx responsesAdds additional input validation to enhance security in Cloudflare Fonts
2 details in Everything
exec() is now available for Containers
Jun 18, 2026
· release notes
Adds exec() method to Cloudflare Containers for running processes inside a Container from code
Adds this.ctx.container.exec() API to start processes, stream I/O, and inspect exit codes in Cloudflare Containers
1 detail in Everything
Create PlanetScale Postgres and MySQL databases, billed to your Cloudflare account
Jun 18, 2026
· release notes
Cloudflare adds managed PlanetScale Postgres and MySQL databases billed via Cloudflare account.
Allows creating PlanetScale Postgres and MySQL databases directly from the Cloudflare dashboard. Bills PlanetScale database usage as a line item on the existing Cloudflare invoice.
2 details in Everything
Bringing more agent harnesses and frameworks to Cloudflare, starting with Flue (2026-06-17)
Jun 17, 2026
·
issue 001
Cloudflare Agents SDK gains durable execution, sandboxed code execution, a virtual filesystem, and dynamic workflows for production agent harnesses agent harnesses The software around an AI agent that manages its tools, execution loop, state and limits. It determines how the model's proposed actions are run and checked.
└──▷ USE IT
Resume a long-running agent turn automatically after a process crash, preserving expensive intermediate results so the agent doesn't restart from zero.
typescript
copy
import { Agent } from "agents";
import type { FiberRecoveryContext } from "agents";
class MyAgent extends Agent {
async doWork() {
await this.runFiber("my-task", async (ctx) => {
const step1 = await expensiveOperation();
ctx.stash({ step1 });
const step2 = await anotherExpensiveOperation(step1);
this.setState({ ...this.state, result: step2 });
});
}
async onFiberRecovered(ctx: FiberRecoveryContext) {
if (ctx.name !== "my-task") return;
const { step1 } = (ctx.snapshot ?? {}) as { step1?: unknown };
if (step1) {
const step2 = await anotherExpensiveOperation(step1);
this.setState({ ...this.state, result: step2 });
}
}
}
Scaffold a Slack channel integration into a Flue project so an agent can receive and respond to Slack events without writing verification and dispatch boilerplate.
copy
$ flue add channel slack
Adds runFiber() , stash() , and onFiberRecovered() APIs to the Agents SDK, enabling agent turns to checkpoint progress in Durable Object SQLite storage and automatically resume after crashes or restarts. Introduces @cloudflare/codemode, wrapping Dynamic Workers, to execute LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code. Ships @cloudflare/shell, a durable virtual filesystem inside a Durable Object backed by SQLite, exposing typed file operations (read, write, edit, search, grep, diff) that agent harnesses can use as tools without container overhead. Introduces @cloudflare/dynamic-workflows, enabling agents to generate and execute durable multi-step pipelines at runtime — with per-step persistence, retries, and resumption after interruption. Announces @cloudflare/workspace (in development), which will keep a Durable Object's virtual filesystem in sync with a Cloudflare Container, enabling seamless escalation from lightweight Workers to a full Linux environment only when needed.
+2 more
show less
Adds first-party support for the Flue open-source agent framework (built on the Pi harness), with a Cloudflare deployment target that maps each agent to its own Durable Object for automatic scaling, isolated storage, and durable execution. Enables Flue's Anywhere Agents channels for Slack, GitHub, Linear, and Discord via pre-configured integrations scaffolded with flue add channel slack, generating a Markdown blueprint for coding-agent-assisted integration.
7 details in Everything
Introducing the Cloudflare One stack: agent-powered deployment (2026-06-17)
Jun 17, 2026
·
issue 001
Cloudflare One Stack delivers agent-ready skill files for Zero Trust deployment, migration, and troubleshooting automation.
└──▷ HOW TO FIND IT
Load the migration skill into your agent to automatically translate Zscaler Private Access apps and policies into Cloudflare Access — no manual re-entry.
📍 In your agent's skill configuration, add the cloudflare-one-migration skill from the Cloudflare Skills repository, then prompt: 'Migrate all Zscaler Private Access applications to Cloudflare Access and generate a summary of what requires manual review.'
Pair the cloudflare-one skill with the MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
📍 In your agent's skill configuration, add the cloudflare-one skill from the Cloudflare Skills repository and connect the Cloudflare code mode MCP server, then prompt: 'Inventory my existing VPN applications and produce a recommended Cloudflare Tunnel deployment sequence that minimizes cutover disruption.'
Introduces the Cloudflare One Stack: two structured skill files (cloudflare-one and cloudflare-one-migration) that give AI agents curated knowledge, decision trees, and tool definitions to configure, deploy, and manage Cloudflare One environments. Adds VPN VPN A virtual private network, an encrypted tunnel between devices or networks. It carries traffic across another network as though the endpoints had a private connection. Adds vendor-to-vendor migration logic for Zscaler and Palo Alto Networks, including automated translation of Zscaler Private Access application definitions, user groups, and policies into Cloudflare Access equivalents — the same logic used in Cloudflare's Descaler and Deskope programs. Enables network diagram interpretation and generation so agents can visualize proposed topology changes before any configuration is applied. Includes a Digital Experience Monitoring (DEX) toolkit so agents can report on user stability, investigate anomalies in secure web gateway HTTP logs, build remediation rules, and take actions to improve user latency.
+2 more
show less
Supports integration with the Cloudflare code mode MCP server to give agents a typed, live interface to the Cloudflare API — querying accounts, inspecting configurations, and executing Cloudflare-recommended workflows rather than ad-hoc API calls. Available to Cloudflare partners as well as direct customers, enabling faster customer deployments and more accurate troubleshooting without a scheduled engagement.
7 details in Everything
Manage Artifacts from the Cloudflare dashboard
Jun 17, 2026
· release notes
Cloudflare dashboard adds UI for managing Artifacts namespaces, repos, and tokens
Enables viewing, creating, forking, and searching repositories within a namespace directly from the dashboard. Allows provisioning of scoped Git access tokens access tokens A credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions.
2 details in Everything
Post-quantum ML-DSA certificates for Authenticated Origin Pulls and Custom Origin Trust Store
Jun 17, 2026
· release notes
Cloudflare adds Post-quantum Post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA. ML-DSA ML-DSA NIST's main post-quantum digital signature standard (FIPS 204), formerly Dilithium. It is the planned replacement for RSA and ECDSA signatures on certificates and code.
Adds ML-DSA (FIPS 204 FIPS 204 NIST's main post-quantum digital signature standard (FIPS 204), formerly Dilithium. It is the planned replacement for RSA and ECDSA signatures on certificates and code. Authenticated Origin Pulls at zone-level and per-hostname scopes for Cloudflare-to-origin mTLS mTLS Mutual TLS, an encrypted connection where both client and server present certificates to prove their identity. It helps services verify who they are communicating with. Adds ML-DSA certificate authority upload to Custom Origin Trust Store for validating origin server certificates in Full (strict) encryption mode
2 details in Everything
Cloudflare DMARC Management is now generally available (2026-06-16)
Jun 16, 2026
·
issue 001
Cloudflare DMARC Management reaches GA with IP-level threat investigation, unified auth record analysis, and SPF SPF An email authentication standard that lets a domain owner publish, via DNS, which mail servers are authorized to send on its behalf, so receiving servers can reject spoofed senders.
└──▷ HOW TO FIND IT
Enable DMARC Management for a domain and begin receiving aggregate reports to identify unauthorized senders.
📍 In the Cloudflare dashboard, go to your domain › Email › DMARC Management, then follow the setup wizard to start receiving DMARC reports.
Investigate a suspicious sending source IP to determine whether it is a forgotten legitimate vendor or a threat actor spoofing your domain.
📍 In the Cloudflare dashboard, go to your domain › Email › DMARC Management › (select a sending source) › open the Investigate tab to view reputation, geolocation, ASN, and known threat associations for that IP.
Audit your SPF record to find which include: chains are consuming the most lookups before your SPF silently breaks with a permerror.
📍 In the Cloudflare dashboard, go to your domain › Email › DMARC Management › SPF record card › drill into the SPF lookup audit to see each mechanism's lookup cost and your total against the 10-lookup limit.
Adds an Investigate tab per sending source IP that surfaces Cloudflare threat intelligence — reputation, geolocation, ASN ASN Autonomous System Number — a globally unique identifier assigned by regional internet registries to a network operator, letting routing protocols distinguish which organization controls a block of IP addresses. New unified email authentication record status view shows pass/warning/fail for DMARC, SPF, DKIM DKIM An email authentication standard that lets a sending mail server cryptographically sign outgoing messages so receiving servers can verify the signature was not forged or tampered with in transit. New SPF lookup audit traces every DNS lookup incurred by an SPF record — including nested include: chains — and flags when you are approaching or exceeding the RFC 7208 10-lookup limit. DMARC Management is now generally available at no additional cost for all Cloudflare customers with DNS hosted on Cloudflare.
4 details in Everything
Workers tracing now supports custom spans
Jun 16, 2026
· release notes
Cloudflare Workers tracing now supports custom spans via tracing.enterSpan()
Adds tracing.enterSpan() method to create manual trace spans in Workers code. Exposes the tracing object via the cloudflare:workers module (import { tracing } from "cloudflare:workers") or handler context (ctx.tracing). Provides span.setAttribute(key, value) for attaching metadata and span.isTraced property to check sampling status.
3 details in Everything
TCP connections via connect() over VPC Networks
Jun 16, 2026
· release notes
Cloudflare Workers VPC VPC A logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware. TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. connect() on VPC bindings
Adds connect() Socket API to Workers VPC Network bindings for raw TCP connections to private destinations Enables TCP-based protocols (Redis, Memcached, MQTT) over Cloudflare Tunnel, Mesh, and WAN on-ramp in addition to existing HTTP via fetch()
2 details in Everything
Agents SDK improves browser automation, code execution, and recovery
Jun 16, 2026
· release notes
Cloudflare Agents SDK v0.16.1 adds browser_execute CDP CDP Cisco Discovery Protocol, a Cisco-proprietary Layer 2 protocol that advertises device identity, capabilities, and topology between directly connected Cisco gear, giving cyber tools a passive way to map network infrastructure. createCodemodeRuntime, client tools for Think, and voice output routing.
Adds the browser_execute tool (via createBrowserTools) that lets agents write code against the Chrome DevTools Protocol (CDP) for browser automation Introduces createCodemodeRuntime to enable resumable code execution with durable logs and approval-gated actions in Code Mode Enables client-provided tools in Think sub-agents via the clientTools and onClientToolCall parameters on the chat() RPC RPC Remote Procedure Call, a protocol that lets a program execute a function on another machine as if it were local, giving cyber tools a structured way to communicate across processes or hosts without managing raw sockets. Adds outputDeviceId parameter to useVoiceAgent and client.setOutputDevice() method for voice output device selection
4 details in Everything
GLM-5.2 agentic coding model now available on Workers AI with function calling function calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions.
Adds @cf/zai-org/glm-5.2 model to Workers AI for agentic coding workflows Enables function calling and step-by-step reasoning capabilities in the new GLM-5.2 model
2 details in Everything
Cloudflare Images adds composite option, percentage width overlays, aspect-crop/scale-up fit modes, and AI upscale parameter.
Adds composite parameter to control how overlays are blended with the base image Supports percentage widths for overlay dimensions as a fraction of the base image Adds aspect-crop and scale-up fit modes to control aspect ratio preservation and enlargement Adds upscale parameter to apply AI upscaling when enlarging images
4 details in Everything
WAF - Use Cloudforce One threat intelligence in WAF rules (2026-06-15)
Jun 15, 2026
·
issue 014
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ TRY IT
Block inbound requests from IPs linked to DDoS DDoS Distributed Denial of Service: an attack that floods a target system with traffic from many sources simultaneously, exhausting its resources so legitimate requests cannot be served.
copy
$ any(cf.intel.ip.target_countries[*] == "FR") and any(cf.intel.ip.datasets[*] == "ddos")
Adds cf.intel.ip.* fields populated from Cloudforce One threat intelligence, enabling WAF custom and rate-limiting rules to act on IPs flagged within the past seven days. New cf.intel.ip.datasets field identifies whether a flagged IP was associated with DDoS or WAF attack activity. New cf.intel.ip.attacker_names and cf.intel.ip.attacker_countries fields expose known threat actor identities and source countries for use in rule expressions. New cf.intel.ip.target_industries and cf.intel.ip.target_countries fields allow rules to prioritize defense based on the sectors or regions an IP has historically targeted. Threat intelligence matches are recorded in Security Analytics and fully supported via the Cloudflare API and Terraform.
5 details in Everything
WAF - WAF Release - 2026-06-15 (2026-06-15)
Jun 15, 2026
·
issue 014
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. CMS CMS A web content management system for creating and managing digital content without writing code directly; cyber tools use CMS platforms to host documentation, portals, or reporting dashboards quickly. SQLi SQLi An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does.
└──▷ HOW TO FIND IT
Enable the new obfuscated boolean SQLi rule (shipped as Disabled) to actively block evasion attempts against your zone.
📍 In the Cloudflare dashboard, go to Security › WAF › Managed Rules › Cloudflare Managed Ruleset, search for rule ID 6c64b68ef5ed45e7a622cdaab56f403f (SQLi - Obfuscated Boolean - URI), and change its action from Disabled to Block.
New managed rule 439c4ef64b32447989bdf412b4c29bc6 detects and blocks blind SQL injection SQL injection An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does. New managed rule 6c64b68ef5ed45e7a622cdaab56f403f identifies generic SQLi bypass attempts using obfuscated boolean logic in URI parameters (currently set to Disabled).
2 details in Everything
WAF - Use Cloudforce One threat intelligence in WAF rules (2026-06-15)
Jun 15, 2026
·
issue 003
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ TRY IT
Block inbound requests from IPs linked to DDoS DDoS Distributed Denial of Service: an attack that floods a target system with traffic from many sources simultaneously, exhausting its resources so legitimate requests cannot be served.
copy
$ any(cf.intel.ip.target_countries[*] == "FR") and any(cf.intel.ip.datasets[*] == "ddos")
Adds cf.intel.ip.* fields populated from Cloudforce One threat intelligence, enabling WAF custom and rate-limiting rules to act on IPs flagged within the past seven days. New cf.intel.ip.datasets field identifies whether a flagged IP was associated with DDoS or WAF attack activity. New cf.intel.ip.attacker_names and cf.intel.ip.attacker_countries fields expose known threat actor identities and source countries for use in rule expressions. New cf.intel.ip.target_industries and cf.intel.ip.target_countries fields allow rules to prioritize defense based on the sectors or regions an IP has historically targeted. Threat intelligence matches are recorded in Security Analytics and fully supported via the Cloudflare API and Terraform.
5 details in Everything
WAF - WAF Release - 2026-06-15 (2026-06-15)
Jun 15, 2026
·
issue 003
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. CMS CMS A web content management system for creating and managing digital content without writing code directly; cyber tools use CMS platforms to host documentation, portals, or reporting dashboards quickly. SQLi SQLi An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does.
└──▷ HOW TO FIND IT
Enable the new obfuscated boolean SQLi rule (shipped as Disabled) to actively block evasion attempts against your zone.
📍 In the Cloudflare dashboard, go to Security › WAF › Managed Rules › Cloudflare Managed Ruleset, search for rule ID 6c64b68ef5ed45e7a622cdaab56f403f (SQLi - Obfuscated Boolean - URI), and change its action from Disabled to Block.
New managed rule 439c4ef64b32447989bdf412b4c29bc6 detects and blocks blind SQL injection SQL injection An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does. New managed rule 6c64b68ef5ed45e7a622cdaab56f403f identifies generic SQLi bypass attempts using obfuscated boolean logic in URI parameters (currently set to Disabled).
2 details in Everything
WAF - WAF Release - 2026-06-15 (2026-06-15)
Jun 15, 2026
·
issue 002
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. CMS CMS A web content management system for creating and managing digital content without writing code directly; cyber tools use CMS platforms to host documentation, portals, or reporting dashboards quickly. SQLi SQLi An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does.
└──▷ HOW TO FIND IT
Enable the new obfuscated boolean SQLi rule (shipped as Disabled) to actively block evasion attempts against your zone.
📍 In the Cloudflare dashboard, go to Security › WAF › Managed Rules › Cloudflare Managed Ruleset, search for rule ID 6c64b68ef5ed45e7a622cdaab56f403f (SQLi - Obfuscated Boolean - URI), and change its action from Disabled to Block.
New managed rule 439c4ef64b32447989bdf412b4c29bc6 detects and blocks blind SQL injection SQL injection An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does. New managed rule 6c64b68ef5ed45e7a622cdaab56f403f identifies generic SQLi bypass attempts using obfuscated boolean logic in URI parameters (currently set to Disabled).
2 details in Everything
WAF - Use Cloudforce One threat intelligence in WAF rules (2026-06-15)
Jun 15, 2026
·
issue 002
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ TRY IT
Block inbound requests from IPs linked to DDoS DDoS Distributed Denial of Service: an attack that floods a target system with traffic from many sources simultaneously, exhausting its resources so legitimate requests cannot be served.
copy
$ any(cf.intel.ip.target_countries[*] == "FR") and any(cf.intel.ip.datasets[*] == "ddos")
Adds cf.intel.ip.* fields populated from Cloudforce One threat intelligence, enabling WAF custom and rate-limiting rules to act on IPs flagged within the past seven days. New cf.intel.ip.datasets field identifies whether a flagged IP was associated with DDoS or WAF attack activity. New cf.intel.ip.attacker_names and cf.intel.ip.attacker_countries fields expose known threat actor identities and source countries for use in rule expressions. New cf.intel.ip.target_industries and cf.intel.ip.target_countries fields allow rules to prioritize defense based on the sectors or regions an IP has historically targeted. Threat intelligence matches are recorded in Security Analytics and fully supported via the Cloudflare API and Terraform.
5 details in Everything
Use Cloudforce One threat intelligence in WAF rules
Jun 15, 2026
· release notes
Adds Cloudforce One threat intelligence fields (cf.intel.ip.*) to WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ HOW TO FIND IT
Block requests from IPs associated with DDoS DDoS Distributed Denial of Service: an attack that floods a target system with traffic from many sources simultaneously, exhausting its resources so legitimate requests cannot be served.
📍 any(cf.intel.ip.target_countries[*] == "FR") and any(cf.intel.ip.datasets[*] == "ddos")
Adds cf.intel.ip.datasets field populated with threat intelligence data for matched IP addresses in WAF rules Adds cf.intel.ip.target_industries, cf.intel.ip.attacker_names, cf.intel.ip.attacker_countries, and cf.intel.ip.target_countries fields to WAF rule expressions Enables use of the any() function with [ * ] wildcard to match array values in these new intelligence fields within custom rules and rate limiting rules
3 details in Everything
Scaling Security Insights: how we achieved a 10x increase in global scanning capacity (2026-06-12)
Jun 12, 2026
·
issue 001
Cloudflare Security Insights now scans all accounts automatically, with frequency doubled across all plans.
Enables automatic Security Insights scanning for all free-plan accounts and zones — previously opt-in only. Doubles (or better) scanning frequency for every plan tier: free accounts scanned every 7 days, Pro/Business every 3 days, and Enterprise daily. Sustains over 120 scans per second at peak, exceeding the 10x throughput improvement target and enabling near-real-time misconfiguration detection at scale.
3 details in Everything
View the user agent of requests in AI Gateway logs
Jun 12, 2026
· release notes
AI Gateway logs now capture and allow filtering by client user agent
Adds user_agent field to AI Gateway log entries Adds user agent filtering (equals, does not equal, contains) in the Cloudflare Dashboard
2 details in Everything
Cloudflare Terraform v5.20 adds 24 new resources for AI, DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Adds cloudflare_ai_search_namespace resource to manage AI Search namespaces Adds cloudflare_custom_csr resource to manage custom certificate signing requests Adds cloudflare_dls_prefix_binding resource to manage DLS regional service prefix bindings Adds cloudflare_flagship_app resource to manage Flagship feature flag apps Adds cloudflare_flagship_flag resource to manage Flagship feature flags
+23 more
show less
Adds cloudflare_google_tag_gateway resource to manage Google Tag Gateway Adds cloudflare_load_balancer_monitor_group resource to manage load balancer monitor groups Adds cloudflare_oauth_client resource to manage IAM IAM Identity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access. Adds cloudflare_origin_cloud_region resource to manage origin cloud regions (v2 endpoints) Adds cloudflare_secrets_store resource to manage Secrets Store instances Adds cloudflare_secrets_store_secret resource to manage Secrets Store secrets Adds cloudflare_share resource to manage resource shares Adds cloudflare_share_recipient resource to manage share recipients Adds cloudflare_share_resource resource to manage shared resources Adds cloudflare_zero_trust_device_deployment_groups resource to manage Zero Trust device deployment groups Adds cloudflare_zero_trust_dlp_data_class resource to manage DLP data classes Adds cloudflare_zero_trust_dlp_data_tag resource to manage DLP data tags Adds cloudflare_zero_trust_dlp_data_tag_category resource to manage DLP data tag categories Adds cloudflare_zero_trust_dlp_sensitivity_group resource to manage DLP sensitivity groups Adds cloudflare_zero_trust_dlp_sensitivity_level resource to manage DLP sensitivity levels Adds cloudflare_zero_trust_dlp_sensitivity_level_order resource to manage DLP sensitivity level ordering Adds cloudflare_zero_trust_resource_library_application resource to manage Zero Trust resource library applications Adds cloudflare_zero_trust_resource_library_category resource to manage Zero Trust resource library categories Adds cloudflare_zero_trust_tunnel_warp_connector_config resource to manage WARP connector tunnel configurations Adds POST method support for smart_tiered_cache to create new cache configurations Updates OPCR config to use v2 endpoints Promotes DLP Stainless classification config to main Adds custom prompt topics endpoint for DLP
28 details in Everything
Moonshot AI Kimi K2.7 Code now available on Workers AI
Jun 12, 2026
· release notes
Moonshot AI Kimi K2.7 Code now available on Workers AI with @cf/moonshotai/kimi-k2.7-code model ID
Adds @cf/moonshotai/kimi-k2.7-code model ID to Workers AI for coding and agentic workloads Adds configurable reasoning depth via chat_template_kwargs.thinking in model parameters Adds vision input support for processing images alongside text in Kimi K2.7 Code
3 details in Everything
Track Dynamic Workers usage from the dashboard and GraphQL API
Jun 11, 2026
· release notes
New Dynamic Workers invocation count visible in dashboard and via distinctDynamicWorkerCount in GraphQL API
Adds workersInvocationsByOwnerAndScriptGroups query with distinctDynamicWorkerCount to the GraphQL Analytics API for tracking Dynamic Workers usage Displays billed Dynamic Worker invocation counts directly on the Workers overview page in the Cloudflare dashboard
2 details in Everything
Define custom topics for AI prompt protection
Jun 11, 2026
· release notes
Introduces custom AI prompt topics for Cloudflare DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Adds Custom Prompt Topic creation in Zero Trust > Data loss prevention > Detection entries to detect unique concepts via natural language description Extends AI prompt protection coverage to ChatGPT, Google Gemini, Perplexity, and Claude with custom topic detection
2 details in Everything
New formats parameter for the Browser Run /snapshot endpoint
Jun 11, 2026
· release notes
Browser Run /snapshot endpoint now supports a formats parameter to return screenshot, Markdown, and accessibility tree in one call
Adds the formats parameter to the Browser Run /snapshot endpoint to request multiple page formats (screenshot, markdown, accessibilityTree) in a single API response
1 detail in Everything
Route public traffic to private applications with Cloudflare (2026-06-10)
Jun 10, 2026
·
issue 001
Cloudflare launches Application Services for Private Origins, routing public traffic to private IPs via WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ TRY IT
Expose an internal API at a private IP behind Cloudflare's full WAF and bot management stack — no public IP or cloudflared on the origin needed.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/zones/{zone_id}/dns_records' \
-H 'Authorization: Bearer <token>' \
-H 'Content-Type: application/json' \
-d '{
"type": "A",
"name": "app.example.com",
"content": "10.0.0.50",
"ttl": 300,
"proxied": true,
"use_private_routing": true
}' Put Cloudflare Spectrum in front of a private SSH or TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it.
copy
$ curl -X POST 'https://api.cloudflare.com/client/v4/zones/{zone_id}/spectrum/apps' \
-H 'Authorization: Bearer <token>' \
-H 'Content-Type: application/json' \
-d '{
"protocol": "tcp/22",
"dns": { "type": "CNAME", "name": "ssh.example.com" },
"origin_direct": ["tcp://10.0.0.50:22"],
"virtual_network_id": "fab9ac85-491b-44c8-b7ae-dd44d4f4672e"
}'
New Application Services for Private Origins (closed beta, Enterprise) lets public hostnames resolve to RFC 1918 RFC 1918 IETF standard that reserves three IPv4 address ranges (10.x, 172.16–31.x, 192.168.x) for private networks, never routed on the public internet, giving tools a reliable way to identify internal traffic. IPsec IPsec A suite of IETF protocols that authenticate and encrypt IP packets at the network layer, giving cyber tools a standards-based way to build VPNs or secure host-to-host tunnels without modifying applications. GRE GRE A tunneling protocol that wraps one network packet inside another, letting tools carry arbitrary traffic across IP networks without modifying the payload, useful for traffic capture and network emulation. Enables WAF, bot management, rate limiting, caching, transform rules, and Workers in front of private-origin applications without deploying cloudflared on the origin host. New use_private_routing field on DNS A/AAAA records (auto-enabled for private IP ranges, manually togglable for others) signals Cloudflare's proxy to route the final hop through the customer's private network connectivity. Spectrum (Layer 4 proxy) now supports TCP/UDP UDP A network protocol that sends individual messages without guaranteeing delivery or order. Applications trade built-in reliability for less overhead and can add their own recovery. virtual_network_id field on origin configuration, routing through Cloudflare Tunnel without a load balancer intermediary. Workers VPC VPC A logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware.
+1 more
show less
Cloudflare's private networking routing layer is unified across Cloudflare Tunnels, Virtual Networks, Mesh, and WAN — customers manage routing behavior through a single API/dashboard instead of separate per-product stacks.
6 details in Everything
Flagship API reference now available
Jun 10, 2026
· release notes
Cloudflare Flagship API reference now available for managing apps and feature flags via REST.
Adds API support for updating, deleting, and listing feature flags without dashboard use
1 detail in Everything
Automated Cease and Desist templates for Brand Protection
Jun 10, 2026
· release notes
Brand Protection adds automated Cease & Desist template generation with pre-filled WHOIS data and custom-branding.
Adds a Generate C&D Letter document builder in the Brand Protection dashboard for domains hosted on external providers Introduces three default layout strategies (Exact Match, Similar Match, Friendly Tone) to tailor enforcement tones
2 details in Everything
Manage AI Search namespaces with Wrangler CLI
Jun 10, 2026
· release notes
Wrangler CLI gains ai-search namespace subcommands and --json output for automated namespace management.
└──▷ TRY IT
Filter instance-level AI search results to a specific namespace.
copy
$ wrangler ai-search list --namespace docs-production
Adds five new CLI commands: wrangler ai-search namespace list, create, get, update, and delete Adds --json flag to list, create, get, and update commands for structured automation output Adds --namespace flag to instance-level wrangler ai-search list command to scope queries
3 details in Everything
Manage hosted images with the Images binding
Jun 10, 2026
· release notes
Introduces the env.IMAGES.hosted namespace in Cloudflare Workers for direct image management via bindings.
Adds the env.IMAGES.hosted binding namespace to Worker scripts for managing hosted images.
1 detail in Everything
Defend against frontier cyber models: Cloudflare's architecture as customer zero (2026-06-09)
Jun 9, 2026
·
issue 001
Cloudflare adds Cloudforce One threat intel in WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. MCP Server MCP Server A process that exposes tools, resources, and prompts over Anthropic's Model Context Protocol, letting an AI agent call external APIs or local services through a standardised interface.
└──▷ HOW TO FIND IT
Enforce that no newly shipped internal tool is reachable on the network before an Access policy exists — critical when developers are moving fast with AI-assisted coding.
📍 In the Cloudflare Zero Trust dashboard, go to Settings › Access › and enable Require Access Protection so any application deployed without a policy is blocked by default.
Centralize SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management.
📍 In the Cloudflare dashboard, go to Zero Trust › Settings › Authentication › IdP Federation, configure your identity provider once, and enable federation — new recipient accounts receive SSO automatically with read-only IdP connections.
Give AI agents controlled, audited access to enterprise systems through approved MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
📍 In the Cloudflare dashboard, go to AI › MCP Server Portal, register your MCP servers, and connect agents through the portal — every agent action is logged with what it did and what it touched.
Enables Cloudforce One threat intelligence directly within the WAF, allowing customers to block high-risk traffic from tracked adversaries and emerging campaigns without waiting for external feed propagation. Introduces Require Access Protection to ensure newly deployed or misconfigured internal applications cannot be reached before an Access policy is in place. Adds IdP Federation to share a single identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. Launches MCP Server Portal, a centralized management plane for connecting AI agents to enterprise systems via approved MCP servers, with full action logging for auditability. Extends AI Security for Apps scoring methodology to internal AI tooling via AI Gateway, providing visibility into what engineers are building with AI before policies are written.
5 details in Everything
Turning Cloudflare’s threat indicators into real-time WAF rules (2026-06-08)
Jun 8, 2026
·
issue 001
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
└──▷ TRY IT
Block IPs from Cloudflare's DDoS DDoS Distributed Denial of Service: an attack that floods a target system with traffic from many sources simultaneously, exhausting its resources so legitimate requests cannot be served.
copy
$ any(cf.intel.ip.target_countries[*] == "FR") and any(cf.intel.ip.datasets[*] == "ddos") Protect a financial application by blocking traffic from a known ransomware group targeting the banking sector, driven by live threat-actor attribution.
copy
$ any(cf.intel.ip.target_industries[*] == "Banking & Financial Services") and any(cf.intel.ip.attacker_names[*] == "BLACKBASTA")
New WAF fields (cf.intel.ip.attacker_names, cf.intel.ip.target_industries, cf.intel.ip.attacker_countries, cf.intel.ip.target_countries, cf.intel.ip.datasets) expose Cloudflare Threat Events intelligence directly in custom WAF rule expressions. Always-on detection runs threat-intelligence enrichment in the background on every HTTP request, surfacing threat metadata in Security Analytics regardless of whether a blocking rule is active. Supports array-matching via any() and [*] wildcard, allowing a single rule to evaluate multiple simultaneous threat actor associations or targeted industries per IP. Threat Events intelligence fields are fully supported via the Cloudflare API and Terraform for Infrastructure-as-Code WAF custom rules and rate limiting. One-click WAF rule creation from the Threat Events dashboard lets analysts export Saved Views (e.g., 'IPs attacking Financial sector in last 7 days') directly into a WAF rule without manual copy-paste.
+3 more
show less
Threat-intelligence lookups are distributed to every Cloudflare data center as compressed datasets with O(1) constant-time lookup, adding effectively zero latency. Roadmap: planned extension of threat matching to JA3 JA3 A method for fingerprinting TLS clients by hashing fields from the ClientHello message, producing a short string that identifies the TLS library or application making a connection regardless of IP or port. Requires an active Cloudforce One subscription (Essentials, Advantage, or Elite tiers) with varying access to datasets and analyst insights.
8 details in Everything
R2 SQL now supports UNION, INTERSECT, EXCEPT, and SELECT DISTINCT
Jun 8, 2026
· release notes
R2 SQL adds UNION, UNION ALL, INTERSECT, EXCEPT, and SELECT DISTINCT support.
Adds UNION, UNION ALL, INTERSECT, and EXCEPT set operations to R2 SQL queries for combining result sets from multiple SELECT statements Adds SELECT DISTINCT support to eliminate duplicate rows from query results
2 details in Everything
Authenticated SMTP submission now available in beta
Jun 8, 2026
· release notes
Cloudflare Email Service adds authenticated SMTP SMTP The application-layer protocol used to send email between servers and from clients to servers; cyber tools use it to relay alerts, phishing simulations, or exfiltrated data over standard mail infrastructure. smtp.mx.cloudflare.net:465
Enables sending email via smtp.mx.cloudflare.net:465 using PLAIN or LOGIN authentication with an API token as username.
1 detail in Everything
Introducing Threat Actor Profiles in Threat Events
Jun 8, 2026
· release notes
Cloudflare introduces Threat Actor Profiles in Threat Events to provide immediate Who, Why, and How context for security teams.
Threat Actor Profiles provide aliases, origin tracking, historical volume, and MITRE ATT&CK MITRE ATT&CK A publicly maintained knowledge base of adversary tactics and techniques observed in real attacks, maintained by MITRE. Cyber tools use it as a common taxonomy to classify, map, and communicate threat behavior.
1 detail in Everything
Create WAF rules directly from Threat Events saved views
Jun 8, 2026
· release notes
Cloudflare enables direct WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Post-meeting transcriptions are now Generally Available in RealtimeKit
Jun 8, 2026
· release notes
Cloudflare RealtimeKit adds post-meeting transcription and AI summary capabilities with webhook/API delivery
Adds transcribe_on_end flag to the create-meeting API to auto-generate transcript files after a meeting ends Adds summarize_on_end flag to the create-meeting API to enable AI-generated meeting summaries via Whisper Large v3 Turbo Introduces meeting.transcript and meeting.summary webhook events for real-time notification of completed transcription results Adds /sessions/{session_id}/transcript and /sessions/{session_id}/summary GET endpoints to fetch transcript and summary files manually Supports CSV, JSON, SRT, and VTT output formats for post-meeting transcripts
5 details in Everything
Your AI bill is out of control. Cloudflare can fix it now. (2026-06-05)
Jun 5, 2026
·
issue 001
Cloudflare AI Gateway adds dollar-based spend limits and identity-driven budgets with Cloudflare Access integration.
└──▷ TRY IT
Set a monthly dollar budget for a specific team by scoping a spend limit to a custom attribute in the AI Gateway dashboard or API.
copy
$ curl -X POST https://api.cloudflare.com/client/v4/accounts/<account_id>/ai-gateway/gateways/<gateway_id>/spend-limits \
-H 'Authorization: Bearer <api_token>' \
-H 'Content-Type: application/json' \
-d '{
"limit": 500,
"currency": "USD",
"window": "monthly",
"window_type": "fixed",
"attributes": {"team": "interns"},
"on_exceed": "block"
}' Route requests to a cheaper fallback model automatically when a spend limit is hit, so engineer workflows aren't interrupted.
📍 # In AI Gateway dashboard: Settings › Spend Limits › Add Limit
# Set limit: $5000/month, scope: provider=anthropic, model=claude-opus
# On exceed: Dynamic Route → fallback to workers-ai/llama-3
# Or via API, set on_exceed: route with a configured Dynamic Route fallback target
Enroll in the identity-driven budgets closed beta to tie per-user and per-IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. JWT JWT An open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object passed between parties. Cyber tools use it to verify identity and permissions without querying a central session store.
📍 In the Cloudflare dashboard: AI Gateway › your gateway › Identity & Budgets › Enable Cloudflare Access integration
→ Create an Access application scoped to your AI Gateway endpoint
→ Configure policies mapped to your existing IdP groups (e.g., ml-team → Claude Opus + GPT-4o, interns → Workers AI open-source models)
→ Each authenticated request will have email, IdP group, and service token name attached to its log entry
Adds spend limits to AI Gateway: dollar-denominated budgets (not token-based) scoped by model, provider, or custom attributes like user, team, or application. Supports fixed and rolling budget windows — daily, weekly, or monthly — with real-time cumulative spend tracking per request. Enables fallback routing via Dynamic Routes when a spend limit is reached, preventing hard blocks from disrupting engineer workflows. New analytics dashboard filtering lets teams track model spend by model, provider, or any custom attribute. Introduces identity-driven budgets and routing (closed beta) via Cloudflare Access integration: per-user, per-IdP-group, and per-service-token spend policies derived from authenticated JWT identity.
+2 more
show less
Supports named identities for CI/CD pipelines and autonomous agents via Access service tokens, enabling per-agent budget policies and token usage attribution. Every AI Gateway log entry now includes authenticated identity (email, IdP group, service token name) for export to external analytics platforms.
7 details in Everything
Rollback support now available in Workflows
Jun 5, 2026
· release notes
Cloudflare Workflows adds saga-style rollback support with per-step compensating logic and rollbackConfig.
Adds rollback option to step.do() calls for adding compensating logic to each step in case of downstream failures Adds rollbackConfig to step.do() for configuring retry limits, delays, backoff strategies, and timeouts for rollback handlers Exposes rollback outcomes in instance status responses for debugging production workflows
3 details in Everything
AI Gateway introduces spend limits with configurable budgets scoped by model, provider, or metadata.
AI Gateway now supports spend limits that track cumulative dollar spend and block requests when the budget is exceededSpend limits can be scoped by model, provider, or custom metadata dimensions
2 details in Everything
Filter Workers' public Internet traffic using Gateway policies
Jun 5, 2026
· release notes
Cloudflare Workers egress through Gateway via VPC VPC A logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware. EGRESS binding for Zero Trust policy enforcement
Share identity providers across accounts with IdP federation
Jun 4, 2026
· release notes
Cloudflare Access now supports IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. identity providers identity providers A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems.
Billable usage and budget alerts now in product sidebars
Jun 4, 2026
· release notes
Billable usage and budget alerts now available directly in product sidebars for Workers, D1, R2, KV, Queues, Vectorize, DO, and Containers.
Adds a new sidebar widget to the overview pages for Workers & Pages, D1, R2, Workers KV, Queues, Vectorize, Durable Objects, and Containers showing current-period spend and billing cycle date range. Adds an inline Create budget alert flow from product sidebars that allows setting a dollar threshold for account-level spend without leaving the product page.
2 details in Everything
Store Wrangler's OAuth credentials in your OS keychain
Jun 3, 2026
· release notes
Wrangler adds --use-keyring flag to store OAuth credentials in OS keychain instead of plaintext TOML
└──▷ TRY IT
Opt in to storing Wrangler credentials securely in the OS keychain during login.
copy
$ npx wrangler login --use-keyring Verify where your credentials are currently stored after changing configuration.
Adds the --use-keyring flag to wrangler login to opt into AES-256-GCM AES-256-GCM AES encryption in Galois/Counter Mode, which encrypts data and detects tampering in one pass. It is the default cipher for TLS and most disk and cloud encryption. Adds support for the CLOUDFLARE_AUTH_USE_KEYRING environment variable to override keyring behavior per-command or globally. Updates wrangler whoami output to display the current credential storage location (keychain vs plaintext file).
3 details in Everything
SAML assertion encryption for identity providers
Jun 3, 2026
· release notes
Cloudflare Access introduces SAML SAML A standard for passing signed identity assertions between a sign-in provider and an application. It lets a user sign in through their organization's identity provider. identity providers identity providers A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems.
Adds the ability to encrypt SAML assertions transmitted through the user's browser using a Cloudflare-managed certificate Introduces automatic certificate generation when enabling SAML encryption for an identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. Provides certificate rotation capabilities allowing overlap between old and new certificates to prevent downtime Enables PEM format export of the encryption certificate or points IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems.
4 details in Everything
New Workers bulk secrets API endpoint
Jun 3, 2026
· release notes
Cloudflare Workers introduces wrangler secret bulk CLI command and a new API endpoint for bulk secrets management.
Adds the /accounts/:account_id/workers/services/:service_name/secrets/bulk API endpoint to create, update, or delete multiple Worker secrets in a single HTTP request.
1 detail in Everything
Introducing self-managed OAuth clients
Jun 3, 2026
· release notes
Cloudflare introduces self-managed OAuth clients via a new Dashboard menu for third-party app integration.
Adds a new OAuth clients section under Manage account > OAuth clients in the Cloudflare dashboard to create and manage third-party applications.
1 detail in Everything
Agents SDK v0.14.0: Agent Skills, messengers, scheduled tasks, Workflows, and hardened chat recovery
Jun 2, 2026
· release notes
Agents SDK v0.14.0 introduces Agent Skills, Telegram messengers, scheduled tasks, ThinkWorkflows, and hardened chat recovery with isRecovering.
Adds getSkills() method to Think agents for on-demand skill catalogs via the agents:skills import Adds defineMessengers() helper and @cloudflare/think/messengers/telegram module for Telegram bot integration Adds getScheduledTasks() method with a typed DSL for declaring timezone-aware recurring prompts Adds ThinkWorkflow class and step.prompt() for model-driven reasoning inside Cloudflare Workflows Adds isRecovering flag to useAgentChat hook to expose recovery state in UIs
+3 more
show less
Adds chatStreamStallTimeoutMs configuration to handle stalled model provider streams Adds optional id parameter to addMcpServer() for readable Server IDs Adds virtualModules option to @cloudflare/worker-bundler's createWorker function
8 details in Everything
Schedule Workflow instances directly from your Workflow binding
Jun 2, 2026
· release notes
Attach cron schedules directly to Workflow bindings in wrangler.jsonc
Cloudflare WAN third-party integration guide for Cisco IOS XE updated with PQC PQC Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA. SLA SLA A formal agreement between a service provider and customer that defines expected uptime, response times, and remedies for failures, giving cyber tools a contractual baseline for availability and support commitments.
Documentation update for Cisco IOS XE integration adds Post Quantum Cryptography (PQC) guidance
1 detail in Everything
New Turnstile Events Logpush dataset in Cloudflare Logs
Jun 1, 2026
· release notes
Cloudflare Logs now includes a new Turnstile Events Logpush dataset with 14 fields for bot challenge telemetry.
Adds the Turnstile Events dataset to Cloudflare Logs Logpush, enabling push-based delivery of human/bot interaction telemetry Exposes 14 specific log fields in the new dataset including ASNASN Autonomous System Number — a globally unique identifier assigned by regional internet registries to a network operator, letting routing protocols distinguish which organization controls a block of IP addresses. Action , BrowserMajor, BrowserName, ClientIP, CountryCode, EventType, Hostname , OSMajor , OSName , Sitekey , Timestamp , and UserAgent
2 details in Everything
Updated fields across multiple Logpush datasets in Cloudflare Logs
May 29, 2026
· release notes
New fields added to DEX Device State Events, Gateway HTTP, and HTTP requests Logpush datasets.
Adds DeviceRegistrationProfileID field to the DEX Device State Events dataset Adds AddedHeaders, DeletedHeaders, and SetHeaders fields to the Gateway HTTP dataset Adds MatchedRules field to the HTTP requests dataset
3 details in Everything
Security Insights scans run by default on all accounts with granular on-demand scan support.
Adds Granular on-demand scans for any plan, zone, insight, or insight type triggered from the Cloudflare dashboard Makes Security Center scans default for all accounts and zones (Free: every 7 days, Pro/Business: every 3 days, Enterprise: daily) Removes the requirement to manually enable scans before Cloudflare checks for misconfigurations
3 details in Everything
D1 migrations support nested layouts via `migrations_pattern`
May 29, 2026
· release notes
D1 migrations add migrations_pattern to support nested migration file layouts
Adds migrations_pattern config key to the D1 binding in Wrangler to discover nested migration files. Allows wrangler d1 migrations apply to process nested migration structures like Drizzle's default output.
2 details in Everything
Cloudflare's Realtime WebSocket adapter now auto-reconnects and buffers WebRTC media
May 29, 2026
· release notes
Cloudflare Realtime WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output. WebRTC WebRTC A browser-native, open standard for real-time peer-to-peer audio, video, and data exchange without plugins. Cyber tools use it to tunnel traffic or exfiltrate data through connections browsers treat as legitimate.
Adds automatic reconnection logic to the WebSocket adapter in Stream mode (egress), retrying the same endpoint for up to 5 seconds after brief disconnects or restarts. Enables live-first media buffering during reconnection, using a short bounded backlog for audio and resuming video from the latest available JPEG frame.
2 details in Everything
Cloudflare One Client for macOS (version 2026.5.1155.1)
May 29, 2026
· release notes
Cloudflare One Client for macOS 2026.5.1155.1 adds VNET scoping in device profiles, file-based emergency disconnect, and DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit.
Administrators can now control which virtual networks (VNETs) are available to which users via WARP device profile settings in the Zero Trust dashboard Added a local-file signal source for Emergency Disconnect. In addition to the existing HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate. The local DNS proxy now supports DNSSEC passthrough. DNSSEC-signed responses are forwarded to the application intact (including DO/AD bits and RRSIG records), so applications that validate DNSSEC locally — including resolvers and the dig/drill tooling — work correctly through the client. Added a new MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies. FedRAMP FedRAMP A US government program that standardizes cloud security authorization, letting vendors get a single assessment accepted across federal agencies instead of repeating the process for each one. Client Certificate device-posture checks now support template variables (e.g. ${serial_number}, ${device_uuid}) in the Subject Alternative Name field
5 details in Everything
Share sandbox previews through Cloudflare Tunnel
May 29, 2026
· release notes
The Cloudflare Sandbox SDK now supports sharing internal services via Cloudflare Tunnel. New sandbox.tunnels namespace allows zero-config quick tunnels or persistent named tunnels for container previews.
Adds sandbox.tunnels.get(port) to automatically create a zero-config *.trycloudflare.com quick tunnel from inside a sandbox container Adds sandbox.tunnels.get(port, { name }) option to create a persistent named Cloudflare Tunnel with a custom CNAME CNAME A DNS record type that maps one hostname to another as a canonical alias, letting cyber tools track infrastructure by following chains of names to their true origin.
2 details in Everything
Cloudflare One Client for Windows (version 2026.5.1155.1)
May 29, 2026
· release notes
Cloudflare One Client for Windows 2026.5.1155.1 adds mandatory auth, WNET scoping, DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit.
Adds mandatory authentication to block all Internet traffic until user authenticates Enables VNET scoping in Zero Trust dashboard device profiles so users only see scoped networks Supports DNS search suffixes from device profile / network policy for single-label queries Adds local-file signal source for Emergency Disconnect via a monitored disk file Introduces new warp-cli debug commands for interactive connection diagnosis
+4 more
show less
Enables DNSSEC passthrough in the local DNS proxy, forwarding DO/AD bits and RRSIG records Supports template variables (e.g. ${serial_number}) in Client Certificate device-posture SAN fields Adds a new MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies. Restores support for the UseWebView2 registry key (HKLM\SOFTWARE\Cloudflare\CloudflareWARP\UseWebView2) to enforce embedded WebView2 browser for sign-in
9 details in Everything
TLS bug detection in the Cloudflare Radar post-quantum checker
May 29, 2026
· release notes
Cloudflare Radar PQ checker now detects TLS handshake bugs (Split ClientHello, HRR Failure, Unknown Keyshare) via API
Adds detection of HRR Failure bugs during post-quantum post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA. Adds detection of Unknown Keyshare bugs where servers fail to respond with HelloRetryRequest for unknown key exchange algorithms Adds detection of Split ClientHello bugs involving fragmented post-quantum ClientHello messages
3 details in Everything
Tool and prompt aliases for MCP server portals
May 28, 2026
· release notes
Adds tool and prompt aliases for MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds the ability to rename tools and prompts and rewrite their descriptions directly on the portal without modifying the upstream server. Adds a Modified label in the tools list to indicate which tools have been customized. Allows setting aliases at two levels: per portal (takes precedence over server-level) and per server.
3 details in Everything
Send emails with named recipient addresses
May 28, 2026
· release notes
Cloudflare Email Service now supports display names on recipient addresses via object syntax
Adds name field support to the to, cc, and bcc fields of env.EMAIL.send() for displaying recipient names in email clients Extends from field in env.EMAIL.send() to accept an object with email and name fields instead of a plain string
2 details in Everything
Record specific participant audio tracks in RealtimeKit
May 28, 2026
· release notes
RealtimeKit adds selective track recording via POST /recordings/track with user_ids support for per-participant WebM files.
Adds POST https://api.cloudflare.com/client/v4/accounts/<account_id>/realtime/kit/<app_id>/recordings/track endpoint to start track recordings for specific participants Supports user_ids JSON array field in request body to specify which participant audio tracks to record separately as WebM files
2 details in Everything
R2 Data Catalog gets a dedicated dashboard experience
May 28, 2026
· release notes
R2 Data Catalog now has a dedicated Cloudflare Dashboard with a guided setup wizard, metrics tabs, and snapshot expiration controls.
Adds a dedicated R2 Data Catalog section in the Cloudflare dashboard replacing the embedded bucket settings panel Adds a three-step guided setup wizard for catalog creation including automatic service credential generation Adds a snapshot expiration configuration option directly in the dashboard to control compaction and expiry
3 details in Everything
└──▷ BREAKING ON UPGRADE
! The previous settings panel embedded in R2 bucket configuration is replaced by the dedicated catalog section
Wrangler supports SSH ProxyCommand for Containers
May 28, 2026
· release notes
Wrangler v2.x adds wrangler containers ssh as an OpenSSH ProxyCommand for container access.
Adds the --stdio flag to wrangler containers ssh to force stdin/stdout forwarding mode. Enables using wrangler containers ssh %h as a named ProxyCommand in OpenSSH configurations.
2 details in Everything
Use Browser Run Quick Actions directly from Workers
May 28, 2026
· release notes
New quickAction() method on browser binding lets Workers call Browser Run screenshots, PDFs, and extraction directly.
Adds quickAction() method on the browser binding to invoke Browser Run Quick Actions (screenshots, PDFs, content extraction) directly from a Worker without API tokens Requires compatibility_date of 2026-03-24 or later in Wrangler config to enable the new browser binding functionality
2 details in Everything
High availability replica management for Cloudflare Mesh
May 28, 2026
· release notes
Cloudflare Mesh dashboard adds per-replica HA details, badges, and manual failover via the Networking > Mesh UI
Adds Replica tabs on the node detail page to view Mesh IP, edge data center, origin IP, platform, version, and uptime for each replica Adds Active/passive badges in the overview table to identify which replica is currently routing traffic Adds HA badge in the overview table to identify nodes running multiple replicas Shows Active replica IP in the overview table Adds manual failover capability via Promote to active action on a passive replica tab
5 details in Everything
Cloudflare Tunnel now runs connectivity pre-checks at startup
May 27, 2026
· release notes
cloudflared v2026.5.2 adds automated connectivity pre-checks at startup for DNS, UDP UDP A network protocol that sends individual messages without guaranteeing delivery or order. Applications trade built-in reliability for less overhead and can add their own recovery. TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it.
Cloudflare Tunnel cloudflared binary runs native DNS resolution checks for region1.v2.argotunnel.com and region2.v2.argotunnel.com at startup. Adds outbound transport connectivity verification for UDP (QUIC QUIC A UDP-based transport protocol standardized by the IETF that bakes in TLS 1.3, multiplexed streams, and connection migration, giving tools low-latency encrypted transport without head-of-line blocking. api.cloudflare.com, directly in the startup flow. New CLI output includes actionable remediation hints (e.g., Allow outbound UDP on port 7844 ) for Fail/Warn states, exiting early on blocking failures instead of looping.
3 details in Everything
Cloudflare One Client for macOS (version 2026.4.1390.0)
May 26, 2026
· release notes
Cloudflare One Client for macOS GA adds MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies.
└──▷ TRY IT
Manually trigger an MDM policy pull from the command line.
copy
$ warp-cli mdm refresh
Adds warp-cli mdm refresh subcommand to immediately refresh MDM configuration Introduces a new built-in captive portal login experience in the macOS UI
2 details in Everything
Cloudflare One Client for Windows (version 2026.4.1390.0)
May 26, 2026
· release notes
Cloudflare One Client for Windows GA adds new UI, warp-cli mdm refresh, and captive portal login
└──▷ TRY IT
Immediately apply updated MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies.
copy
$ warp-cli mdm refresh
Adds the first general availability of the new Cloudflare One Client UI for Windows with a cleaner design and right-click context menu. Adds the warp-cli mdm refresh CLI command to execute an immediate refresh of the Mobile Device Management configuration file. Adds a built-in captive portal login experience.
3 details in Everything
Cloudflare Flagship enables serverless feature flag management via Workers KV and Durable Objects.
Cloudflare One Client for Linux (version 2026.4.1390.0)
May 26, 2026
· release notes
Cloudflare One Client for Linux GA adds new UI and warp-cli mdm refresh CLI command
warp-cli mdm refresh CLI command to immediately refresh MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies. New Cloudflare One Client UI for Linux with right-click context menu and captive portal login Official support for RHEL RHEL Red Hat Enterprise Linux, a commercially supported Linux distribution maintained by Red Hat, chosen by cyber tools for its long support lifecycle, certified hardware compatibility, and enterprise deployment prevalence.
3 details in Everything
BYPASS status now returned for uncacheable responses
May 26, 2026
· release notes
Cloudflare now consistently returns BYPASS cache status for uncacheable responses, separating them from MISS in analytics.
Cache status BYPASS is now returned for all uncacheable responses (e.g., exceeding max file size, Cache-Control: no-cache, Set-Cookie , Authorization header), replacing the previous inconsistent mix of BYPASS and MISS. MISS is now reserved exclusively for cacheable responses that were not in the local cache at request time, improving accuracy of cache hit ratio calculations.
2 details in Everything
Call any AI model through AI Gateway's new REST API
May 21, 2026
· release notes
Cloudflare AI Gateway adds a unified REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Introduces POST /ai/run, POST /ai/v1/chat/completions, POST /ai/v1/responses, and POST /ai/v1/messages endpoints on api.cloudflare.com for unified AI model access. Enables third-party model requests to be billed through Unified Billing, eliminating the need to manage separate provider API keys.
2 details in Everything
Modernized Billing Profile with new payment options
May 21, 2026
· release notes
New unified Billing Profile with Subscriptions tab and Apple Pay/Google Pay support
Introduces the Subscriptions tab in the Billing Profile to unify billing info, payment methods, and subscriptions. Adds Apple Pay, Google Pay, Link, and Instant Bank Payments via Link as payment options.
2 details in Everything
Reach Cloudflare WAN destinations from Workers VPC
May 21, 2026
· release notes
Workers can now route requests to Cloudflare WAN destinations via VPC VPC A logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware.
Adds network_id: "cf1:network" binding support in VPC Networks config to reach private network services from Workers
1 detail in Everything
Granular permissions for Cloudflare Tunnel and Cloudflare Mesh
May 21, 2026
· release notes
Cloudflare introduces granular permissions scoped to individual Tunnel and Mesh nodes via resource picker and new API filtering.
Cloudflare Tunnel instances and Cloudflare Mesh nodes are now listed as scopable resource types when adding a member or creating a permission policyListing endpoints return only resources the principal has at least read access to, changing the surface of enumeration for GET /accounts/{id}/cfd_tunnel and GET /accounts/{id}/warp_connector
2 details in Everything
Content type distribution and API traffic share on Cloudflare Radar
May 20, 2026
· release notes
Cloudflare Radar adds Content Type Distribution and API Traffic Share charts with new HTTP endpoints filters.
Adds Content type distribution chart on the Radar traffic page showing HTTP response content type groups Adds API traffic share chart displaying percentage of dynamic API-related requests in Radar traffic views Exposes CONTENT_TYPE dimension and contentType filter on HTTP summary, timeseries groups, and timeseries endpoints Exposes API_TRAFFIC dimension and apiTraffic filter (values API, NON_API) on HTTP summary, timeseries groups, and HTTP timeseries endpoints
4 details in Everything
Cloudflare rolls out refreshed DNS records UX with resizable columns, logical filters, and mobile support
Adds resizable and hideable columns, row pinning, advanced filters with logical operators (AND/OR), configurable pagination, and expanded input fields to the DNS records page in the Cloudflare dashboard Introduces a first-class mobile experience with responsive layout, touch-friendly card-based UI, and compact controls for small screens Adds DNS quick reference explainers for DNS, proxy status, and TTL TTL Time to live, a limit on how long data remains valid or how far a packet can travel. Caches use a time limit; IP packets use a hop limit.
3 details in Everything
Cloudflare Radar adds MRT Explorer in Routing section for browser-based BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
Adds MRT Explorer tool in the Radar Routing section for analyzing BGP announcements, withdrawals, and route attributes from MRT dump files entirely in the browser without uploading data. Supports loading MRT files via URL paste, drag-and-drop, or local file browse, including Gzip and bzip2 compressed formats, with a sample file provided to get started. Enables inspecting BGP events by timestamp, prefix, AS path, OTC (Only to Customer), and community attributes, with full event JSON available via View details modal. Generates shareable URLs containing the source file query string so recipients can immediately fetch and parse the same MRT file in their browser.
4 details in Everything
Event subscriptions for Artifacts lifecycle events
May 19, 2026
· release notes
Event subscriptions for Cloudflare Artifacts lifecycle events (repo.created, pushed, etc.)
Adds artifacts and artifacts.repo sources to receive event notifications for repository changes. Enables triggering Worker workflows on Account-level events: repo.created, repo.deleted, repo.forked, repo.imported. Enables triggering Worker workflows on Repository-level events: pushed, cloned, fetched.
3 details in Everything
CASB adds support for Claude Compliance API
May 19, 2026
· release notes
Cloudflare CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic. DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Adds Claude Compliance API integration to ingest audit logs and administrative actions from Claude Enterprise and Claude Platform Adds scanning for Project attachment (files/documents violating DLP policies) in public projects Adds scanning for Chat files (user-uploaded and provider-generated files violating DLP policies) Adds scanning for Chat messages (prompts/responses violating DLP policies) Adds scanning for Artifacts (provider-generated documents/files violating DLP policies)
5 details in Everything
Cloudflare as identity provider and account membership selector
May 19, 2026
· release notes
Cloudflare Access now supports Cloudflare as an IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems.
Adds support for using Cloudflare as an identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. Introduces a new Cloudflare Account Member selector policy that matches users based on their membership in a Cloudflare account.
2 details in Everything
Manage Artifacts namespaces and repos with Wrangler CLI
May 18, 2026
· release notes
Wrangler CLI gains subcommands to manage Artifacts namespaces and repos
Adds wrangler artifacts namespaces list command to list Artifacts namespaces in an account Adds wrangler artifacts namespaces get command to retrieve metadata for a specific namespace Adds wrangler artifacts repos create command to create a new repo within a namespace Adds wrangler artifacts repos list command to list all repos inside a namespace Adds wrangler artifacts repos get command to retrieve metadata for a specific repo
+2 more
show less
Adds wrangler artifacts repos delete command to remove a repo from a namespace Adds wrangler artifacts repos issue-token command to issue a repo-scoped token for Git access
7 details in Everything
Network Analytics support for Unified Routing
May 18, 2026
· release notes
Network Analytics now supports traffic visibility for accounts using Unified Routing mode.
Traffic traversing Unified Routing onramps and offramps is now visible in the Network Analytics dashboard with standard dimensions and filters.
1 detail in Everything
Hyperdrive exposes database connection pool size metrics
May 15, 2026
· release notes
Hyperdrive now exposes database connection pool size metrics via UI chart and GraphQL API
Adds a Pool connections chart in the Cloudflare dashboard to visualize waiting clients, open connections, and pool size maximum for Hyperdrive configurations Exposes hyperdrivePoolSizesAdaptiveGroups dataset in the GraphQL Analytics API with fields currentPoolSize, availablePoolSlots, waitingClients, and maxPoolSize
2 details in Everything
R2 SQL now supports JOINs, subqueries, and multi-table queries
May 15, 2026
· release notes
R2 SQL now supports JOINs, subqueries, CTEs, self-joins, and multi-way joins for complex analytical queries.
INNER JOIN, LEFT JOIN, RIGHT JOIN, FULL OUTER JOIN, CROSS JOIN, and implicit comma-separated joins enable combining multiple Iceberg tablesIN/NOT IN, EXISTS/NOT EXISTS, scalar subqueries in SELECT/WHERE/HAVING, and derived tables in FROM provide advanced filtering and transformation logicMulti-table CTEs allow WITH clauses to reference different tables and include JOINs within a single query Self-joins allow joining a table with itself using different aliases Multi-way joins support joining three or more tables in a single query
5 details in Everything
New Domains tab in the Workers dashboard
May 14, 2026
· release notes
New Domains tab in the Workers dashboard for unified domain purchase, connection, and routing management.
Enables toggling workers.dev subdomain and Preview URLs on or off within the new Domains interface. Allows enabling Cloudflare Access for authentication on workers.dev subdomains and Preview URLs via the Domains tab. Provides direct navigation links to analytics and domain overview from any connected domain in the Domains tab.
3 details in Everything
New Logpush datasets and updated fields across multiple Logpush datasets in Cloudflare Logs
May 13, 2026
· release notes
Cloudflare Logs adds new Logpush datasets and AI security fields
Adds the Email Security Post-Delivery Events dataset with fields like AlertID, Destination, and FinalDisposition Adds the Magic Network Monitoring Flow Logs dataset with fields like AWSVPCFlowJSON, SourceAddress, and TcpFlags Adds AI security scoring fields to existing datasets Adds AI security scoring fields to existing Firewall events dataset
4 details in Everything
Agents SDK v0.12.4: chat recovery, routing retries, durable Think submissions, and Voice connection control
May 13, 2026
· release notes
Cloudflare Agents SDK v0.12.4 adds routing retries, Voice enabled flag, and durable Think submissions
Adds routingRetry configuration option to getAgentByName() for handling transient Durable Object failures Adds enabled boolean option to useVoiceAgent() to control VoiceClient connection lifecycle Adds submitMessages() function in @cloudflare/think for durable, idempotent server-driven turns
3 details in Everything
└──▷ BREAKING ON UPGRADE
! ChatOptions.tools has been removed from the TypeScript API; define durable tools on the child agent or use agent tools for orchestration instead! @cloudflare/think no longer applies pruneMessages({ toolCalls: 'before-last-2-messages' }) to model context by default
Cloudflare Access login page refreshed with unified card, consistent styling, mobile improvements and dark mode support
Unified authentication card groups all sign-in options (identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. OTP OTP One-time password: a short-lived numeric or alphanumeric code valid for a single authentication attempt, generated via TOTP or HOTP standards, giving cyber tools phishing-resistant second-factor verification without stored shared secrets. Consistent button styling applies uniform size and layout to identity provider buttons for easier scanning Better mobile experience with responsive layout improvements for phones and tablets
3 details in Everything
R2 Data Catalog now exposes metrics via the GraphQL Analytics API
May 12, 2026
· release notes
R2 Data Catalog now exposes Iceberg API and maintenance metrics via two new GraphQL Analytics datasets.
Exposes r2CatalogDataOperationsAdaptiveGroups dataset to track Iceberg REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Exposes r2CatalogTableMaintenanceAdaptiveGroups dataset to track table maintenance jobs such as compaction and snapshot expiration success rates and metrics. Both new datasets support filtering by warehouse name, namespace, table name, and time range, with percentile aggregations for duration metrics.
3 details in Everything
SSH through Wrangler is now enabled by default for Containers
May 12, 2026
· release notes
SSH through Wrangler is now enabled by default for Containers; no config change needed to use wrangler containers ssh.
└──▷ TRY IT
Connect to a Container instance immediately after deployment without updating the config file.
copy
$ wrangler containers ssh <INSTANCE_ID>
The ssh.enabled config key defaults to true for Containers, removing the previous requirement to explicitly enable it
1 detail in Everything
Agent Readiness scores now available in URL Scanner via the Cloudflare Dashboard
May 12, 2026
· release notes
New Agent Readiness tab in URL Scanner provides six scores for AI agent optimization.
Adds an Agent Readiness tab to URL Scanner reports in the Cloudflare Dashboard showing Basic Web Presence, Discoverability, Content Accessibility, Bot Access Control, Protocol Discovery, and Commerce scores Enables retrieval of Agent Readiness scores via the URL Scanner API
2 details in Everything
Create Gateway firewall policies with natural language
May 12, 2026
· release notes
Cloudflare Gateway adds natural language policy creation via Create with AI button for DNS, HTTP, and Network rules
NAT-T support for IKE on UDP port 500
May 11, 2026
· release notes
Cloudflare WAN and Magic Transit now support standard NAT-T for IKE on UDP UDP A network protocol that sends individual messages without guaranteeing delivery or order. Applications trade built-in reliability for less overhead and can add their own recovery.
Adds NAT-T support for IPsec IPsec A suite of IETF protocols that authenticate and encrypt IP packets at the network layer, giving cyber tools a standards-based way to build VPNs or secure host-to-host tunnels without modifying applications.
1 detail in Everything
Cloudflare One Client for macOS (version 2026.4.1350.0)
May 11, 2026
· release notes
Cloudflare One Client for macOS reaches GA with new UI and warp-cli mdm refresh command
└──▷ TRY IT
Force the macOS agent to re-fetch its MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies.
copy
$ warp-cli mdm refresh
warp-cli mdm refresh subcommand added to execute an immediate refresh of the Mobile Device Management (MDM) configuration file
1 detail in Everything
Cloudflare One Client for Windows (version 2026.4.1350.0)
May 11, 2026
· release notes
Cloudflare One Client for Windows GA adds MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies.
└──▷ USE IT
Immediately sync MDM policy changes on a managed Windows endpoint without waiting for the background check interval.
shell
copy
warp-cli mdm refresh
Adds the warp-cli mdm refresh subcommand to trigger an immediate Mobile Device Management configuration refresh on demand. Introduces a right-click context menu in the new Windows UI for quick access to common client actions. Adds a built-in captive portal login experience for Windows users who need to authenticate on network gateways.
3 details in Everything
Cloudflare One Client for Linux (version 2026.4.1350.0)
May 11, 2026
· release notes
Cloudflare One Client for Linux 2026.4.1350.0 adds GA status, new UI, warp-cli mdm refresh command, and RHEL RHEL Red Hat Enterprise Linux, a commercially supported Linux distribution maintained by Red Hat, chosen by cyber tools for its long support lifecycle, certified hardware compatibility, and enterprise deployment prevalence.
warp-cli mdm refresh command added to immediately refresh MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies. RHEL 9 support for Cloudflare Mesh nodes (requires EPEL repository) New Cloudflare One Client UI for Linux with right-click context menu and captive portal login
3 details in Everything
Self-serve provisioning of Cloudflare One Virtual Appliance via API
May 7, 2026
· release notes
New API endpoints allow creating, rotating, and deleting Cloudflare One Virtual Appliance instances via REST calls.
Adds POST /accounts/{account_id}/magic/connectors endpoint with device.provision_license: true to create a virtual appliance instance and receive its license key in the response. Adds PATCH /accounts/{account_id}/magic/connectors/{connector_id} endpoint with provision_license: true to rotate the license key for an existing virtual appliance, revoking the previous key immediately. Enables deletion of virtual appliances via the API, which releases the associated licensed device.
3 details in Everything
Source-based breakout and prioritization on Cloudflare One Appliance
May 7, 2026
· release notes
Cloudflare One Appliance breakout rules now support matching by source LAN interface or IP.
Breakout traffic rules can now match by source in addition to destination applicationBreakout or priority behavior can be pinned to a source LAN interface, automatically including attached VLANs Breakout or priority behavior can be pinned to a source IP address, range, or CIDR CIDR A notation for a block of IP addresses, such as 10.0.0.0/24. The number after the slash says how many leading address bits identify the network.
3 details in Everything
Automatic tracing across Durable Object and Worker subrequests
May 7, 2026
· release notes
Automatic tracing across Durable Object and Worker subrequests now propagates trace context for unified views.
Traces now propagate automatically across Worker-to-Worker subrequests via service bindings, producing a single unified trace view instead of disconnected traces Service binding and Durable Object calls are now recorded as nested child spans within the main trace, enabling debugging of cross-Worker request flows in the Cloudflare dashboard or external OpenTelemetry OpenTelemetry An open standard and set of tools for collecting traces, metrics and logs from applications. It lets services export observability data without tying instrumentation to one monitoring vendor.
2 details in Everything
CSV export and adjustable page density for RFIs
May 7, 2026
· release notes
Cloudflare Security Center adds CSV export for RFI history and configurable page density (10/25/50) to the Requests for Information dashboard.
Adds CSV export capability for RFI history records, enabling download of security center data for external auditing and reporting Introduces adjustable page density setting in the RFI dashboard with options for 10, 25, or 50 records per page
2 details in Everything
TAXII support added to Threat Events API
May 6, 2026
· release notes
Cloudforce One Threat Events API now accepts format=taxii for TAXII TAXII A protocol for sharing threat intelligence over HTTPS, commonly carrying STIX data. It lets tools retrieve and exchange intelligence from compatible services.
└──▷ TRY IT
Ingest Cloudforce One threat events directly into a TAXII-capable SIEM SIEM Security information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents.
copy
$ GET /accounts/{account_id}/cloudforce_one/threat_events?format=taxii
Adds taxii as a supported value for the format query parameter on the Threat Events API endpoint Enables automated ingestion of Cloudforce One threat indicators into SIEM, TIP, and SOAR SOAR Security orchestration, automation and response, coordinating incident workflows across tools. Playbooks can gather evidence, assign work or carry out approved response actions.
2 details in Everything
TLD Nameserver Performance in Cloudflare Radar
May 6, 2026
· release notes
Cloudflare Radar adds TLD TLD The rightmost label in a domain name (e.g., .com, .gov, .uk), maintained by IANA's root zone. Cyber tools filter or pivot on TLDs to scope scans, flag suspicious registrations, or classify traffic by geography or type.
Adds aggregate nameserver latency, per-nameserver median latency, geographic distribution map, and rank change deltas to TLD detail pages in Cloudflare Radar UI Adds /tlds/performance/summary/{dimension} and /tlds/performance/timeseries_groups/{dimension} endpoints to the new TLD Performance API supporting LATENCY, NAMESERVER_LATENCY, and LOCATION_LATENCY dimensions
2 details in Everything
Pipelines and R2 Data Catalog now supported in Terraform
May 4, 2026
· release notes
Terraform provider v5.19.0 adds resources to manage Cloudflare Pipelines and R2 Data Catalog
cloudflare_r2_data_catalog resource added to enable the data catalog on an R2 bucketcloudflare_pipeline_stream resource added to create a stream for HTTP or Worker event ingestioncloudflare_pipeline_sink resource added to configure sinks writing to R2 Data Catalog or R2cloudflare_pipeline resource added to define pipelines connecting streams to sinks via SQL
4 details in Everything
Pingora now powers Cloudflare's cache
May 4, 2026
· release notes
Pingora-based cache introduces async stale-while-revalidate, unbuffered bypass, and stricter Vary/Set-Cookie handling
Adds asynchronous stale-while-revalidate to serve stale content immediately while revalidating in the background. Enables unbuffered bypass by default for responses that bypass cache, streaming directly to the client. Changes Vary: * header handling to bypass cache instead of storing the response. Strips Set-Cookie on cache MISS and EXPIRED responses for previously cached assets.
4 details in Everything
└──▷ BREAKING ON UPGRADE
! Responses with Vary: * are no longer stored in the cache; they bypass cache entirely.! Set-Cookie headers are now stripped on cache MISS and EXPIRED responses for previously cached assets, not just on HITs.
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. XSS XSS Cross-site scripting, an attack that runs malicious script in another user's browser through a trusted site. It can steal data or perform actions using the user's session.
Adds ...f0884a68: XSS, HTML Injection - Object Tag - Body (beta) detection with new action set to Block Adds ...ff012303: XSS, HTML Injection - Object Tag - Headers detection with new action set to Block Adds ...16f921d9: XSS, HTML Injection - Object Tag - URI detection with new action set to Block Adds ...dc90d21a: Command Injection - Generic 9 - Body Vector - Beta detection with new action set to Disabled Adds ...f8960375: Command Injection - Generic 9 - Header Vector - Beta detection with new action set to Disabled
+14 more
show less
Adds ...ef47a800: Command Injection - Generic 9 - URI Vector - Beta detection with new action set to Disabled Adds ...beebf804: Command Injection - Sleep - Body detection with new action set to Disabled Adds ...0d257566: Command Injection - Sleep - Headers detection with new action set to Disabled Adds ...1856fe86: Command Injection - Sleep - URI detection with new action set to Disabled Adds ...e6e43c37: Fortinet FortiSandbox - Command Injection - CVE:CVE-2026-39808 detection with new action set to Block Adds ...88118795: Remote Code Execution - Common Bash Bypass - Headers detection with new action set to Disabled Adds ...9299d53b: Remote Code Execution - Common Bash Bypass - URI detection with new action set to Disabled Adds ...b0bf33f9: Remote Code Execution - Common Bash Bypass - Body - Beta detection with new action set to Disabled Adds ...33bfe8b9: PHP Object Injection - 2 - Body - Beta detection with new action set to Disabled Adds ...29552387: PHP Object Injection - 2 - Headers detection with new action set to Disabled Adds ...8104f4c5: PHP Object Injection - 2 - URI detection with new action set to Disabled Adds ...6a46201e: SQLi - DROP - 2 - Beta detection with new action set to Disabled Adds ...8b7f85ee: SQLi - DROP - 2 - Headers detection with new action set to Disabled Adds ...1546b5f0: SQLi - DROP - 2 - URI detection with new action set to Disabled
19 details in Everything
New routing widgets on Cloudflare Radar
May 4, 2026
· release notes
Cloudflare Radar adds BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
Adds Top ASes by announced IP space chart on country pages to show IPv4/IPv6 IPv6 The current version of the Internet Protocol, standardized by the IETF, using 128-bit addresses to replace the exhausted IPv4 space. Cyber tools target it because modern networks run dual-stack or IPv6-only. Adds RPKI ROA deployment timeseries widget on global, country, and AS views with toggle for prefix vs IP address space coverage Exposes new /bgp/ips/top/ases endpoint on the BGP API for top ASN ASN Autonomous System Number — a globally unique identifier assigned by regional internet registries to a network operator, letting routing protocols distinguish which organization controls a block of IP addresses. Exposes new /bgp/rpki/roas/timeseries endpoint on the BGP API for RPKI ROA validation coverage over time
4 details in Everything
Run Workflows inside Dynamic Workers with the @cloudflare/dynamic-workflows library
May 1, 2026
· release notes
Introduces @cloudflare/dynamic-workflows library to run durable Workflows inside Dynamic Workers.
Adds createDynamicWorkflowEntrypoint, DynamicWorkflowBinding, and wrapWorkflowBinding exports to the @cloudflare/dynamic-workflows module
1 detail in Everything
New predefined detection entries are available
Apr 30, 2026
· release notes
Cloudflare DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest. PII PII Personally Identifiable Information — data that can identify a specific individual, such as names, email addresses, or SSNs. Cyber tools flag or redact it to limit exposure and meet privacy regulations.
Adds new predefined detection entries for specific credential types (GitHub PAT PAT A personal access token, a credential used by scripts and integrations instead of a user's password. Its permissions and expiry depend on the service issuing it. Adds support for detecting webhook URLs (Slack Webhook, Discord Webhook) in Cloudflare DLP. Adds PII detection capabilities for addresses (US Physical Address), tax identifiers, and national IDs. Adds detection for financial data and crypto wallets (Bitcoin Wallet) in Cloudflare DLP.
4 details in Everything
Dark mode support on Cloudflare Radar
Apr 30, 2026
· release notes
Radar adds a theme selector with Light, Dark, and System options.
Cloud Observatory connection metrics improvements
Apr 30, 2026
· release notes
Cloud Observatory adds provider/region connection metrics and percentile distributions to Radar UI and Origins API
ORIGIN, REGION, and PERCENTILE dimensions now supported in the Origins API timeseries_groups endpointCloud Observatory overview page now shows connection metrics broken down by cloud provider (AWS, GCP, Azure, Oracle Cloud) Provider pages now display connection metrics for the top five regions with a ranking selector (lowest/highest values) Region pages now display connection metrics as percentile distributions (25th, 50th/median, 75th)
4 details in Everything
Web Analytics adds Navigation Type filtering and reporting
Apr 30, 2026
· release notes
Web Analytics adds Navigation Type filtering and reporting for cache analysis
Adds Navigation Type dimension to the Web Analytics dashboard to report and filter navigation behaviors Enables filtering in the dashboard using equals , does not equal , in , or not in matchers on Navigation Type
2 details in Everything
Go SDK v7.0.0 adds Organization Audit Logs API, Browser Rendering targets management, Queues metrics, and nested AI Search filters.
Adds client.Organizations.Logs.Audit new service for querying organization audit logs with cursor-based pagination Adds client.BrowserRendering.Devtools.Browser.Targets.Close() to close a specific browser target by ID Adds client.Queues.GetMetrics() to retrieve queue metrics for a specific queue Adds FiltersObjectFilterUnion and FiltersWorkersObservabilityFilterLeaf types for nested filter groups in Observability telemetry Adds WaitForCompletion parameter to NamespaceInstanceItemNewOrUpdateParams and NamespaceInstanceItemSyncParams in AI Search
5 details in Everything
└──▷ BREAKING ON UPGRADE
! Removed all *SearchForAgents nested types from ai_search package instance metadata structs! Changed path parameter types for Email Security sub-resources from int64 to string for AllowPolicies, BlockSenders, Domains, ImpersonationRegistry, and TrustedDomains! Renamed path parameter from postfixID to investigateID in Email Security Investigate methods! Removed SettingDomainService.BulkDelete method and its associated types! Changed SettingTrustedDomainService.New return type from *SettingTrustedDomainNewResponseUnion to *SettingTrustedDomainNewResponse! Changed InvestigateMoveService.New return type from *[]InvestigateMoveNewResponse to *pagination.SinglePage[InvestigateMoveNewResponse]! Restructured Observability telemetry filter parameter types in workers package to use nested discriminated union types
Post-quantum IPsec interoperability with third-party devices
Apr 30, 2026
· release notes
Cloudflare IPsec IPsec A suite of IETF protocols that authenticate and encrypt IP packets at the network layer, giving cyber tools a standards-based way to build VPNs or secure host-to-host tunnels without modifying applications. post-quantum post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA. ML-KEM ML-KEM NIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake.
Enables hybrid IKEv2 IKEv2 The second version of the Internet Key Exchange protocol, standardized by the IETF, used to negotiate and authenticate IPsec tunnels. Cyber tools build on it for reliable, fast VPN session setup with built-in NAT traversal and EAP support. ML-KEM-768 ML-KEM-768 NIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake. ML-KEM-1024 ML-KEM-1024 NIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake. Validates interoperability between Cloudflare IPsec and Cisco IOS XR Release 26.1.1 on 8000 Series routers for post-quantum key exchange post-quantum key exchange A cryptographic handshake algorithm designed to resist attacks from quantum computers, using math problems like lattices that quantum algorithms cannot efficiently solve, letting tools stay secure against future quantum-capable adversaries. Validates interoperability between Cloudflare IPsec and Fortinet FortiOS 7.6.6+ devices for post-quantum key exchange.
3 details in Everything
Classify sensitive content with Data Classification
Apr 30, 2026
· release notes
Cloudflare adds Data Classification feature for organizing and labeling sensitive content via labels, templates, and reusable data classes.
Introduces Data Classification capability allowing administrators to organize and label sensitive content using labels, templates, and reusable data classes Enables definition of custom labels including sensitivity schemas, levels, data tag groups, and tags Allows building from Cloudflare-managed templates and creating reusable data classes that combine detection entries, other data classes, sensitivity levels, and data tags Permits use of created classifications in custom DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
4 details in Everything
Shared dictionaries passthrough now in open beta
Apr 30, 2026
· release notes
Cloudflare opens shared dictionary passthrough to open beta on all plans.
Adds passthrough mode for shared dictionaries via API and dashboard. Supports Use-As-Dictionary and Available-Dictionary headers in passthrough. Caches delta-compressed Brotli (dcb) and Zstandard (dcz) variants end-to-end.
3 details in Everything
Cloudflare TypeScript SDK v6.0.0 Released
Apr 30, 2026
· release notes
Cloudflare TypeScript SDK v6.0.0 adds 11 new top-level resources including AI Search, Vulnerability Scanner, and Fraud detection APIs
Adds client.aiSearch (46 methods) for managing AI Search instances, namespaces, tokens, and items Adds client.vulnerabilityScanner (21 methods) for initiating and managing vulnerability scans Adds client.fraud (2 methods) for accessing the new Fraud detection API Adds client.connectivity (5 methods) for Directory service APIs via Connectivity resource Adds client.emailSending (7 methods) including send and send_raw endpoints
+6 more
show less
Adds client.googleTagGateway (2 methods) for Google Tag Gateway management Adds client.organizations (8 methods) for Organization profiles and audit logs Adds client.r2DataCatalog (11 methods) for R2 Data Catalog routes Adds client.realtimeKit (54 methods) for Realtime Kit APIs Adds client.resourceTagging (9 methods) for Resource tagging routes Adds client.tokenValidation (13 methods) for Token validation rules
11 details in Everything
└──▷ BREAKING ON UPGRADE
! The file positional argument in client.ai.toMarkdown.transform() is now passed inside the params object! The body positional argument in client.radar.ai.toMarkdown.create() is now passed inside the params object! The first positional argument in client.abuseReports.create() is renamed from reportType to reportParam! The array parameter in client.iam.userGroups.members.create() is renamed from body to members! client.originTLSClientAuth.hostnames.certificates path is now client.originTLSClientAuth.zoneCertificates! client.radar.netflows casing is changed to client.radar.netFlows! 179 methods now return null instead of a typed response object for delete operations! Pagination types changed (e.g., KeysCursorPaginationAfter to KeysCursorLimitPagination) for 17 methods! Response type names changed (e.g., CloudflaredCreateResponse to CloudflareTunnel) for 29 methods
Cloudflare Python SDK v5.0.0 Released
Apr 30, 2026
· release notes
Cloudflare Python SDK v5.0.0 adds 11 new services (e.g. aisearch, r2_data_catalog) and optional aiohttp backend.
└──▷ TRY IT
Install the SDK with optional aiohttp dependencies for async concurrency.
copy
$ pip install cloudflare[aiohttp]
Adds aiohttp backend support via DefaultAioHttpClient() for improved async concurrency Adds pip install cloudflare[aiohttp] as the new installation method for the aiohttp backend Introduces 11 new top-level service clients including aisearch, connectivity, email_sending, fraud, google_tag_gateway, organizations, r2_data_catalog, realtime_kit, resource_tagging, token_validation, and vulnerability_scanner Adds vulnerability_scanner service with support for vulnerability scanning, credential sets, and target environments
4 details in Everything
└──▷ BREAKING ON UPGRADE
! Drops support for Python 3.8; minimum required version is now Python 3.9! Bumps typing-extensions minimum version from >=4.10 to >=4.14
Empty buckets and delete folders from the R2 dashboard
Apr 30, 2026
· release notes
R2 dashboard now supports emptying buckets and deleting folders via UI
Adds Empty button under the Empty Bucket section on the bucket's Settings tab to delete all objects while preserving the bucket. Enables deletion of folders (grouped by prefix when View prefixes as directories is selected) directly from the Objects tab.
2 details in Everything
Cloudflare Link now supports direct bank account payments for US self-serve accounts.
Adds bank account as a payment option in Cloudflare Link checkout alongside existing card payments.
1 detail in Everything
Hyperdrive support for private databases with Workers VPC
Apr 29, 2026
· release notes
Hyperdrive now supports connecting to private databases via Workers VPC VPC A logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware.
Adds --service-id, --database, --user, and --password flags to the wrangler hyperdrive create CLI subcommand for configuring Hyperdrive connections through a Workers VPC. Adds Connect to private database > Workers VPC option in the Cloudflare dashboard UI for creating Hyperdrive configurations backed by a private network.
2 details in Everything
Gateway Authorization Proxy and hosted PAC files are now generally available
Apr 29, 2026
· release notes
Gateway Authorization Proxy and hosted PAC PAC A Proxy Auto-Configuration file, a JavaScript snippet a browser or OS fetches to decide which proxy server to route each request through, letting cyber tools intercept or redirect traffic without per-app configuration.
Adds Gateway Authorization Proxy endpoints that use Cloudflare Access authentication to verify user identity before applying Gateway filtering. Enables creation and distribution of hosted PAC files directly from Cloudflare One on the global network.
2 details in Everything
Digital experience tests to authenticated resources and enhanced configuration
Apr 29, 2026
· release notes
Digital experience tests now support authenticated resources via Cloudflare Access with enhanced HTTP method and header configuration.
Digital experience tests now support testing applications protected by Cloudflare Access or third-party authentication Added DELETE, PATCH, POST, PUT to supported HTTP methods for digital experience tests Added support for Secret Store headers, custom plain text headers, and custom request bodies in test configuration Added advanced settings: follow redirects, response bodies, response headers, and allow untrusted certificates
4 details in Everything
Adds enforce_dns_only API setting for account-wide traffic bypass
Enables the new enforce_dns_only API setting to disable Cloudflare's reverse proxy across all zones simultaneously.
1 detail in Everything
Realtime backlog metrics now available for Queues
Apr 28, 2026
· release notes
Cloudflare Queues now exposes realtime backlog metrics (backlog_count, backlog_bytes, oldest_message_timestamp_ms) via API, JS, and dashboard.
Adds env.QUEUE.metrics() JavaScript method to retrieve realtime backlog data directly from Workers
1 detail in Everything
Direct access to Support from the dashboard
Apr 28, 2026
· release notes
Support button in dashboard navigation now opens Cloudflare Support Portal directly.
Detect PII records with a new predefined DLP profile
Apr 28, 2026
· release notes
Cloudflare introduces a new Personally Identifiable Information (PII) Record predefined DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Personally Identifiable Information (PII) Record predefined DLP profile detects multiple PII PII Personally Identifiable Information — data that can identify a specific individual, such as names, email addresses, or SSNs. Cyber tools flag or redact it to limit exposure and meet privacy regulations.
1 detail in Everything
Cloudflare One Client adds remote speed test metrics via UI in Zero Trust > Insights
Enables IT teams to remotely run speed tests from the Cloudflare One Client to the network edge. Adds download and upload throughput metrics for Internet speed analysis. Adds download, upload, unloaded latency, and jitter metrics for latency assessment. Adds a Network quality score measuring video streaming and webchat/real-time communication (RTC) performance.
4 details in Everything
Internet outage notifications for devices
Apr 28, 2026
· release notes
Digital Experience Monitoring dashboard now displays Internet outage and traffic anomaly notifications for Cloudflare One Client devices.
Create and manage DLP detection entries outside of profiles
Apr 28, 2026
· release notes
Manage DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Adds direct creation and management of DLP detection entries from the Detection entries section, decoupling them from individual profiles
1 detail in Everything
Cloudflare Resource Tagging public beta adds API and UI for tagging resources with custom key-value metadata.
└──▷ HOW TO FIND IT
Navigate the Cloudflare dashboard to view and manage tagged resources for a specific account.
📍 Manage Account › Resource Tagging
Adds Account Owned Tokens authentication support for persistent tag automation across credential rotations Introduces account and zone-level CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. Enables querying tagged resources using AND/OR logic, negation, and key-only matching with up to 20 filters per query
3 details in Everything
Structured error responses for Cloudflare 5xx errors
Apr 27, 2026
· release notes
Cloudflare now returns structured JSON/Problem Details for its own 5xx errors with Retry-After headers
└──▷ USE IT
Check for the Retry-After header on retryable errors like 521 to determine wait time.
shell
copy
curl -s --compressed -D - -o /dev/null -H "Accept: application/json" -A "TestAgent/1.0" -H "Accept-Encoding: gzip, deflate" "<YOUR_DOMAIN>/cdn-cgi/error/521" | grep -i retry-after
Ten Cloudflare-generated 5xx error codes (500, 502, 504, 520-526) now serve structured JSON/Markdown responses following RFC 9457. The error_category field in the response body indicates fault attribution: origin, cloudflare, or ssl.
2 details in Everything
Unified workspace for Brand Protection
Apr 27, 2026
· release notes
Brand Protection now supports a unified workspace with combined query views and multi-tab investigations.
Adds the Combined Matches view that consolidates results from multiple saved queries into a single table for triage Enables opening query extended views in distinct tabs within the Brand Protection dashboard to maintain multiple investigation contexts Adds the Clear Selection action to reset the workspace and pivot between different investigation sets
3 details in Everything
Cache Response Rules now support zone versioning
Apr 27, 2026
· release notes
Cache Response Rules now support zone versioning for safe staging and promotion
Adds Cache Response Rules to Version Management , allowing response-phase settings to be scoped to a version until promoted. Enables independent environment control for response-phase cache behavior (e.g., stripping Set-Cookie headers in staging) via the new versioning workflow.
2 details in Everything
Automate migration from Cloudflare's Terraform v4 to v5 provider
Apr 24, 2026
· release notes
Cloudflare releases tf-migrate CLI to automate migration from Terraform provider v4 to v5
Adds the tf-migrate command-line tool for automated migration of Cloudflare Terraform configurations from provider v4 to v5 Enables automatic resource type renames (e.g., cloudflare_record to cloudflare_dns_record) and attribute transformations (e.g., value to content) Updates cross-file references to renamed resources across the entire configuration Provides a dry-run mode to preview all changes before applying them
4 details in Everything
Network Session Logs now available for all on-ramps
Apr 24, 2026
· release notes
Network Session Logs expanded to Proxy and Browser Isolation on-ramps in Cloudflare Gateway
Generates zero_trust_network_sessions dataset logs for traffic proxied through Proxy endpoints (PAC PAC A Proxy Auto-Configuration file, a JavaScript snippet a browser or OS fetches to decide which proxy server to route each request through, letting cyber tools intercept or redirect traffic without per-app configuration. Generates zero_trust_network_sessions dataset logs for traffic from Browser Isolation egress on-ramps, closing a previous gap in logging coverage
2 details in Everything
Terraform provider v5.19 adds 14 new resources for AI Gateway, Pipelines, and Vuln Scanner.
Adds cloudflare_ai_gateway resource to manage AI Gateway instances Adds cloudflare_certificate_authorities_hostname_associations resource to manage mTLS mTLS Mutual TLS, an encrypted connection where both client and server present certificates to prove their identity. It helps services verify who they are communicating with. Adds cloudflare_custom_page_asset resource to manage custom page assets Adds cloudflare_pipeline resource to manage Cloudflare Pipelines Adds cloudflare_r2_data_catalog resource to manage R2 Data Catalog
+9 more
show less
Adds cloudflare_user_group resource to manage user groups Adds cloudflare_user_group_members resource to manage user group memberships Adds cloudflare_vulnerability_scanner_credential resource to manage vulnerability scanner credentials Adds cloudflare_vulnerability_scanner_credential_set resource to manage vulnerability scanner credential sets Adds cloudflare_vulnerability_scanner_target_environment resource to manage vulnerability scanner target environments Adds cloudflare_workers_observability_destination resource to manage Workers Observability destinations Adds cloudflare_zero_trust_device_ip_profile resource to manage Zero Trust device IP profiles Adds cloudflare_zero_trust_device_subnet resource to manage Zero Trust device subnets Adds cloudflare_zero_trust_dlp_settings resource to manage Zero Trust DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
14 details in Everything
└──▷ BREAKING ON UPGRADE
! cmd/migrate is deprecated in favor of tf-migrate and will be removed in a future release.
Cloudflare Go SDK v6.10.0 adds new services for Vulnerability Scanner, Namespace-scoped AI Search, Browser Devtools, Registrar, Origin Cloud Regions, and DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
client.VulnerabilityScanner.CredentialSets provides full CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information. client.AISearch.Namespaces.Instances.Items.NewOrUpdate() enables instance-item management within namespace-scoped AI Searchclient.BrowserRendering.Devtools.Browser.Protocol() exposes the DevTools protocol endpoint for direct browser control via the BrowserRendering serviceclient.Registrar.Check() (POST /accounts/{account_id}/registrar/domain-check) and client.Registrar.Search() (GET /accounts/{account_id}/registrar/domain-search) allow domain check and search operationsclient.Cache.OriginCloudRegions.BulkEdit() enables bulk editing of origin cloud region configurations
+1 more
show less
client.ZeroTrust.DLP.Settings.Update() allows updating Data Loss Prevention settings within the Zero Trust suite
6 details in Everything
└──▷ BREAKING ON UPGRADE
! InstanceNewParams.TokenID, Type , CreatedFromAISearchWizard, and WorkerDomain are removed from AI Search instance creation parameters! InstanceUpdateParams configuration fields (including IndexMethod, MaxNumResults, etc.) are removed, restructure the update model! InstanceItemService type is removed; use client.AISearch.Namespaces.Instances.Items instead of the non-namespace path! TokenListParams and related types are removed from the ai_search package! Investigate.Move.New() now returns a raw slice (*[]InvestigateMoveNewResponse) instead of a paginated wrapper, and NewAutoPaging() is removed! ConfigEditParams.MTLS and ConfigEditParams.Name are removed from Hyperdrive config parameters! UserGroupMemberNewParams.Body is renamed to UserGroupMemberNewParams.Members! UserGroups.Members.New() now returns a paginated response (*pagination.SinglePage[UserGroupMemberNewResponse]) instead of a single object! Several Pipelines delete methods (e.g., Pipelines.DeleteV1() , Pipelines.Sinks.Delete() ) now return typed responses instead of bare error! Pagination wrappers like SinglePage are removed from Stores and Stream methods; associated AutoPaging() methods are also removed
AAGUID restrictions and AMR matching for Access independent MFA
Apr 23, 2026
· release notes
Access Independent MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. AAGUID AAGUID A 128-bit identifier embedded in a FIDO2/WebAuthn authenticator that identifies the make and model of the device, letting relying parties enforce authenticator policy without tracking individual users. AMR AMR Autonomous Mobile Robot — a self-navigating wheeled platform that maps its environment and plans its own path; cyber tools might target AMR firmware or fleet-management APIs in OT/ICS assessments.
Adds organization-level AAGUID restriction control in Access to limit WebAuthn WebAuthn A web standard that lets a browser prove possession of a passkey or hardware key to a website. It is the browser-facing part of FIDO2 sign-in. FIPS FIPS A set of US federal standards published by NIST that define approved cryptographic algorithms and modules; cyber tools use it to meet compliance requirements in government and regulated environments. Adds AMR matching logic that skips the independent MFA prompt if the identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. amr claim (e.g., hwk, otp, fpt) already satisfies policy requirements.
2 details in Everything
Audit Logs v2 — Organization-level support
Apr 23, 2026
· release notes
New Audit Logs v2 endpoint for retrieving organization-level audit events via API.
R2 Data Catalog snapshot expiration now removes unreferenced data files
Apr 22, 2026
· release notes
R2 Data Catalog snapshot expiration now automatically removes unreferenced data files, reducing storage costs
Snapshot expiration now handles both metadata and data file cleanup automatically during automatic snapshot expiration. Adds npx wrangler r2 bucket catalog snapshot-expiration enable <bucket> subcommand to configure catalog-level snapshot expiration.
2 details in Everything
Custom dashboards available to all customers
Apr 22, 2026
· release notes
Cloudflare makes Custom Dashboards generally available to all customers with unified visibility and expanded limits for Log Explorer users
Logpush subrequest merging for HTTP requests
Apr 21, 2026
· release notes
Adds merge_subrequests config option and Subrequests log field for merging Cloudflare Worker subrequest logs into parent records
Adds merge_subrequests boolean to the http_requests Logpush job configuration to enable nested subrequest logging Adds Subrequests array field to parent http_requests log records when merging is enabled, containing up to 50 merged subrequest objects
2 details in Everything
Country rules supported in Unified Routing
Apr 21, 2026
· release notes
Cloudflare Unified Routing now supports Country rules for geographic access policies
Adds support for creating firewall rules that match traffic based on source or destination country in Unified Routing mode. Enables enforcement of geographic access policies across the network using Country rules.
2 details in Everything
Introducing Billable Usage dashboard and Budget alerts
Apr 21, 2026
· release notes
Pay-as-you-go customers can now monitor billable usage costs via a new dashboard and set spend alerts
New Billable Usage dashboard under Manage Account > Billing provides daily visibility into usage-based costs and sortable breakdowns by product New Budget alerts feature allows setting dollar-based thresholds for account-level usage spend with email notifications when projected spend reaches the threshold
2 details in Everything
WebSocket binary messages now delivered as Blob by default
Apr 21, 2026
· release notes
WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output.
Adds blob delivery for WebSocket binary frames via the websocket_standard_binary_type compatibility flag (default for dates >= 2026-03-17) Allows reverting to ArrayBuffer delivery by setting ws.binaryType = "arraybuffer" before calling accept() Adds no_websocket_standard_binary_type flag to .wrangler/config to force ArrayBuffer as the default for all WebSockets in a Worker
3 details in Everything
└──▷ BREAKING ON UPGRADE
! Binary frames now arrive as Blob instead of ArrayBuffer, causing event.data instanceof ArrayBuffer checks to fail silently for Workers with compatibility dates >= 2026-03-17
Container logs page now includes relevant Worker and Durable Object logs
Apr 21, 2026
· release notes
Container logs page now includes correlated Worker and Durable Object logs with source filtering
Network Overview page in the dashboard
Apr 21, 2026
· release notes
New Network Overview dashboard page for managing Cloudflare Tunnel, Flow, Address Maps, Magic Transit, and WAN.
Adds a new Network Overview page in the Cloudflare dashboard to consolidate network security and connectivity products.
1 detail in Everything
Additional step context and ReadableStream support now available in Workflows step.do()
Apr 21, 2026
· release notes
Cloudflare Workflows adds step context properties and ReadableStream support in step.do()
Adds step.name, step.count, and config (with timeout and retries) to the context object passed to step.do() callbacks for enhanced loop and configuration introspection Enables returning a ReadableStream directly from step.do() handlers to support outputs larger than the previous 1 MiB non-stream limit
2 details in Everything
R2 SQL adds JSON functions, EXPLAIN FORMAT JSON, and unpartitioned table support
Apr 20, 2026
· release notes
R2 SQL adds JSON functions (json_get_str, etc.), EXPLAIN FORMAT JSON, and support for unpartitioned tables
EXPLAIN FORMAT JSON returns query execution plans as structured JSON for programmatic analysisUnpartitioned Iceberg tables can now be queried directly via SQL Adds JSON functions json_get_str, json_get_int, json_get_bool, and json_contains to manipulate JSON data stored in Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS.
3 details in Everything
Cloudflare One adds Network session analytics dashboard for traffic pattern visibility.
Cloudflare Pipelines as a Logpush destination
Apr 20, 2026
· release notes
New capability to route Logpush logs to Pipelines for transformation into Parquet/Iceberg formats.
Moonshot AI Kimi K2.6 now available on Workers AI
Apr 20, 2026
· release notes
Workers AI adds Moonshot AI Kimi K2.6 model with @cf/moonshotai/kimi-k2.6 support
Adds the new @cf/moonshotai/kimi-k2.6 multimodal multimodal Able to work with more than one type of input or output, such as text, images and audio. A multimodal model can combine information across those formats. Supports configurable thinking depth via the chat_template_kwargs.thinking field in API payloads Returns reasoning content in the new reasoning response field, replacing the previous reasoning_content
3 details in Everything
└──▷ BREAKING ON UPGRADE
! The API payload key for controlling thinking is now chat_template_kwargs.thinking, not chat_template_kwargs.enable_thinking! The response field containing reasoning content is now named reasoning, not reasoning_content
AI Insights updates on Cloudflare Radar
Apr 17, 2026
· release notes
Cloudflare Radar AI Insights adds agent standards adoption widget, URL scanner readiness tab, savings gauge, and response status widget.
Adds Adoption of AI agent standards widget to the AI Insights page with domain category filtering Adds Agent readiness tab to URL Scanner reports evaluating URLs against Agent Readiness score criteria Adds savings gauge showing median response-size reduction for Markdown vs HTML served to AI bots Adds response status widget displaying HTTP response code distribution grouped by code or category
4 details in Everything
Smart Tiered Cache optimizes public cloud origins
Apr 17, 2026
· release notes
Smart Tiered Cache now supports public cloud origins via cloud_region_hint on AWS, GCP, Azure, and Oracle Cloud.
Homepage and sign-out for MCP server portals
Apr 17, 2026
· release notes
Adds MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds Homepage to MCP server portals displaying portal name, organization branding, MCP endpoint URL (with copy button), and per-client connection instructions Adds Sign out button to authenticated MCP portal users that revokes all portal-level OAuth grants, deletes upstream server OAuth states, and redirects through Cloudflare Access logout
2 details in Everything
Introducing Redirects for AI Training
Apr 17, 2026
· release notes
Cloudflare introduces AI Crawl Control to redirect verified AI training crawlers to canonical URLs using existing HTML <link rel="canonical"> tags. This feature is available on Pro, Business, and Enterprise plans.
New Redirects for AI Training capability within AI Crawl Control.
1 detail in Everything
AI Search now has hybrid search and relevance boosting
Apr 16, 2026
· release notes
AI Search adds hybrid search hybrid search Combining keyword search with semantic or vector search. The results use both exact term matches and similarity in meaning. BM25 BM25 The classic keyword-ranking formula behind traditional search engines. Hybrid search combines it with embedding similarity so exact terms and meaning both count.
Adds index_method, fusion_method, keyword_tokenizer, and keyword_match_mode to the create call for enabling hybrid search and tuning ranking Adds retrieval.boost_by array in ai_search_options to boost search results by metadata fields like timestamp or priority per request
2 details in Everything
AI Search instances now include built-in storage and namespace Workers Bindings
Apr 16, 2026
· release notes
AI Search now includes built-in storage and new namespace Workers Bindings for dynamic instance management
AI Search instances created after April 16, 2026 include built-in vector index and storage, allowing direct file upload via items.uploadAndPoll and immediate search without external R2 buckets. Adds the ai_search_namespaces binding in wrangler.jsonc, replacing the deprecated env.AI.autorag() API to manage instances at runtime. Enables cross-instance search by passing an array of instance IDs via ai_search_options.instance_ids in the namespace-level search API.
3 details in Everything
└──▷ BREAKING ON UPGRADE
! The env.AI.autorag() API is replaced by the new ai_search_namespaces binding; existing Workers using the old API will require migration to the new binding format.
Artifacts now in beta: versioned filesystem with Git access
Apr 16, 2026
· release notes
Cloudflare Artifacts beta allows creating millions of Git-compatible repos via REST or Workers bindings.
Cloudflare introduces public beta Email Sending with Workers API, Agents SDK integration, and Wrangler CLI commands.
Adds env.EMAIL.send() API to send transactional emails directly from Workers Integrates Email Service with the Agents SDK via a native onEmail hook for receiving and processing email
2 details in Everything
Privacy Proxy metrics now available via GraphQL Analytics API
Apr 15, 2026
· release notes
Cloudflare adds Privacy Proxy metrics (requests, connections, auth) to GraphQL Analytics API
└──▷ TRY IT
Query Privacy Proxy request metrics and dimensions via the GraphQL Analytics API
copy
$ curl https://api.cloudflare.com/client/v4/graphql \
--header "Authorization: Bearer <API_TOKEN>" \
--header "Content-Type: application/json" \
--data '{
"query": "{ viewer { accounts(filter: { accountTag: $accountTag }) { privacyProxyRequestMetricsAdaptiveGroups(filter: { date_geq: $startDate, date_leq: $endDate }, limit: 10000, orderBy: [date_ASC]) { count dimensions { date } } } } }",
"variables": {
"accountTag": "<YOUR_ACCOUNT_TAG>",
"startDate": "2026-04-04",
"endDate": "2026-04-06"
}
}'
Independent MFA for Access applications
Apr 15, 2026
· release notes
Cloudflare Access adds independent MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. TOTP TOTP A one-time password algorithm (RFC 6238) that generates short-lived codes from a shared secret and the current time, giving cyber tools phishing-resistant second-factor authentication without a server round-trip.
Adds Independent MFA capability to Cloudflare Access for organizations to enforce MFA requirements without relying on an identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. Enables per-application and per-policy configuration of MFA settings via Organization, Application, and Policy levels. Supports authenticator types: TOTP applications, Security keys (hardware), and Biometrics (Touch ID, Face ID, Hello) for independent MFA.
3 details in Everything
New TenantID and Firewall for AI fields in Logpush datasets
Apr 15, 2026
· release notes
Cloudflare Logpush datasets now include TenantID and new Firewall for AI fields.
Gateway DNS , Gateway HTTP , Gateway Network , and Zero Trust Network Sessions datasets now include the TenantID field to identify the tenant ID of requests or sessions.Firewall Events and HTTP Requests datasets now include FirewallForAIInjectionScore, FirewallForAIPIICategories, FirewallForAITokenCount, and FirewallForAIUnsafeTopicCategories fields for AI traffic analysis.
2 details in Everything
Browser Run adds Live View, Human in the Loop, and Session Recordings
Apr 15, 2026
· release notes
Browser Run adds Live View, Human-in-the-Loop, and Session Recordings for agent debugging
Adds Live View for real-time visibility of active browser sessions via dashboard, UI, or Chrome DevTools. Adds Human in the Loop capability allowing humans to intervene in live browser sessions during agent execution. Adds Session Recordings by passing recording: true to capture DOM DOM The browser's in-memory tree representation of a web page's structure, standardized by the W3C, giving cyber tools a programmable interface to read or manipulate page content at runtime.
3 details in Everything
Browser Rendering is now Browser Run
Apr 15, 2026
· release notes
Cloudflare Browser Run adds Live View, Human-in-the-Loop, WebMCP, and increases concurrency limits for Workers Paid plans.
Adds Live View to see agent activity in real time Adds Human in the Loop capability for human intervention during automation Adds Session Recordings to replay any session after it ends Adds WebMCP so websites can expose structured tools for AI agents to discover and call directly Increases concurrent browsers per account limit from 30 to 120 for Workers Paid plans
+2 more
show less
Increases new browser instances limit from 30 per minute to 1 per second Redesigns the Browser Run dashboard to show all request types in a single Runs tab
7 details in Everything
Increased concurrency, creation rate, and queued instance limits for Workflows instances
Apr 15, 2026
· release notes
Cloudflare Workflows raises concurrency to 50k instances, creation rate to 300/sec, and queued instances to 2M.
Increases the maximum number of concurrent Cloudflare Workflows instances from 10,000 to 50,000 Raises the instance creation rate limit to 300 per second per account (with a 100 per second per-workflow sub-limit) Increases the maximum queued instances per Workflow from 1 million to 2 million
3 details in Everything
Agent Lee adds Write Operations and Generative UI
Apr 15, 2026
· release notes
Agent Lee adds Write Operations and Generative UI capabilities in Beta
Enables Agent Lee to perform infrastructure changes including updating DNS records, modifying SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination. Adds Generative UI to render inline charts and structured data visualizations within the chat interface using account telemetry
2 details in Everything
New, streamlined creation experience for Access Applications and Gateway Policies
Apr 15, 2026
· release notes
Redesigned Gateway rule builder and streamlined Access application builder with wirefilter editing and preview states.
Adds Wirefilter editing to the Gateway rule builder for viewing and editing rules directly from wirefilter expressions Adds Preview state graphic in the Gateway rule builder to review policy impact before saving Adds Inline policy creation within the self-hosted Access application builder workflow Adds Preview state visualization in the Access application builder to understand policy enforcement before saving
4 details in Everything
Browser Run adds WebMCP support with lab=true query param for structured AI agent tool discovery
Adds lab=true query parameter to /devtools/browser endpoint to enable experimental Chrome beta features including WebMCP support in Browser Run
1 detail in Everything
Introducing Cloudflare Mesh for post-quantum post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA.
Enables post-quantum encrypted networking between enrolled devices and nodes over TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. UDP UDP A network protocol that sends individual messages without guaranteeing delivery or order. Applications trade built-in reliability for less overhead and can add their own recovery. Assigns a private Mesh IP to every enrolled device and node for direct IP-based reachability. Increases the Mesh node limit from 10 to 50 per account. Adds a new dashboard experience at Networking > Mesh with an interactive network map, route configuration, and setup wizard.
4 details in Everything
Manage Browser Rendering sessions with Wrangler CLI
Apr 14, 2026
· release notes
Adds wrangler browser CLI commands to create, manage, and view Browser Rendering sessions.
└──▷ USE IT
Create a browser session lasting 300 seconds and get the connection URL.
shell
copy
wrangler browser create --keepAlive 300
Adds --keepAlive flag to wrangler browser create to set session duration (60-600 seconds) Adds --json support to all wrangler browser commands for structured output structured output Forcing a model's response to match a given format or JSON schema, so software can parse it reliably instead of hoping the text is well formed.
2 details in Everything
VPC Networks and Cloudflare Mesh support now in public beta
Apr 14, 2026
· release notes
Workers VPC VPC A logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware. cf1:network
vpc_networks configuration now accepts binding = "MESH" and network_id = "cf1:network" to route traffic through Cloudflare Mesh.
1 detail in Everything
Logpush to BigQuery — Cloudflare dashboard support
Apr 14, 2026
· release notes
Adds Cloudflare dashboard UI for configuring Logpush jobs to Google BigQuery BigQuery A serverless, cloud-hosted analytical database from Google that runs SQL queries across massive datasets without managing infrastructure, giving cyber tools scalable storage and fast querying over large volumes of log or event data.
Email obfuscation decode script is now non-render-blocking
Apr 14, 2026
· release notes
Email Address Obfuscation decode script now uses the defer attribute for non-blocking loads.
Configure how sensitive data appears in DLP payload logs
Apr 14, 2026
· release notes
New DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Enables incident response validation by preserving character count and visual formatting in Full Mask mode, distinguishing true positives from false positives more effectively than the previous single masking mode
1 detail in Everything
Cloudflare introduces account-level DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Adds Account-level DLP settings configuration capability in Cloudflare One, enabling unified management of OCR OCR Optical character recognition, converting text in an image or scanned document into machine-readable characters. It lets software search or process text that was stored as pixels.
1 detail in Everything
Improved OAuth experience for consent and management
Apr 14, 2026
· release notes
Cloudflare adds per-account OAuth selection, detailed consent screens, and revocation management.
Adds account-by-account selection during OAuth authorization to limit application access scope Enhances OAuth consent screen to display explicit permissions list and application owner details Enables instant revocation of OAuth access via the Profile > Access Management > Connected Applications view
3 details in Everything
Detect Cloudflare API tokens with DLP
Apr 14, 2026
· release notes
Zero Trust DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Adds cfk_ prefixed user-scoped API key detection to the Credentials and Secrets DLP profile Adds cfut_ prefixed user-scoped API token detection to the Credentials and Secrets DLP profile Adds cfat_ prefixed account-scoped API token detection to the Credentials and Secrets DLP profile
3 details in Everything
Generate citations on Cloudflare Radar
Apr 14, 2026
· release notes
Shareable widgets on Cloudflare Radar now include a Generate citation action for research outputs.
Citation modal supports BibTeX, APA, MLA, Chicago, and RIS formats
1 detail in Everything
Secure credential injection and dynamic egress policies for Sandboxes
Apr 13, 2026
· release notes
Adds TLS interception, credential injection, dynamic egress policies to Cloudflare Sandboxes via outboundByHost and setOutboundHandler
Adds MySandbox.outboundByHost property to inject secrets into outbound requests without exposing them to the sandbox workload Adds automatic TLS interception for outbound HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate. Adds allowedHosts and deniedHosts properties on MySandbox to enforce allow/deny lists with glob pattern support Adds setOutboundHandler() method to apply or remove named outbound handlers at runtime without restarting the sandbox Adds params support to dynamic outbound handlers for per-instance customization
5 details in Everything
Local Explorer for local resource data
Apr 13, 2026
· release notes
Local Explorer adds browser UI and REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Adds e terminal shortcut to start Local Explorer during local development sessions Exposes OpenAPI OpenAPI A vendor-neutral specification for describing REST APIs in a machine-readable format, maintained by the OpenAPI Initiative. Cyber tools use it to auto-generate clients, documentation, and validation from a single source of truth. /cdn-cgi/local/explorer/api for programmatic access to local resource data Supports viewing and editing KV, R2, D1, Durable Objects, and Workflows locally via browser or API
3 details in Everything
Containers and Sandboxes are now generally available
Apr 13, 2026
· release notes
Cloudflare Containers and Sandboxes GA with SSH, Sandbox SDK, PTY terminals, and backup/restore APIs
Adds general availability for Cloudflare Containers to run full Linux workloads on the Workers platform Adds Sandbox SDK with a TypeScript API for executing commands, managing files, and exposing services in isolated environments Adds Live preview URLs capability so agents can run long-lived services and verify in-flight changes Adds Persistent code interpreters for Python, JavaScript, and TypeScript within Sandboxes Adds Interactive PTY terminals for real browser-based terminal access with multiple isolated shells per sandbox
+4 more
show less
Adds Backup and restore APIs to snapshot and restore a sandbox workspace Adds Real-time filesystem watching so apps and agents can react immediately to file changes inside a sandbox Adds SSH support to access and debug issues in live containers Adds Docker Hub support for using existing images and registries with Containers
9 details in Everything
Canvas Remoting optimizes performance for productivity applications
Apr 10, 2026
· release notes
Browser Isolation enables Canvas Remoting for vector-based rendering, boosting performance and reducing bandwidth.
Adds Canvas Remoting capability to Browser Isolation, switching HTML5 Canvas updates from rasterized bitmaps to vector draw commands. Adds right-click menu options Disable Canvas Remoting and Enable Canvas Remoting in the isolated webpage background for troubleshooting.
2 details in Everything
API tokens now detectable by secret scanning tools
Apr 10, 2026
· release notes
Cloudflare API tokens now include identifiable patterns that enable secret scanning secret scanning Checking files, code or other data for exposed credentials such as passwords, API keys and tokens. Findings help teams remove the secret and revoke or rotate it.
Browser Rendering adds Chrome DevTools Protocol (CDP) and MCP client support
Apr 10, 2026
· release notes
Browser Rendering adds CDP CDP Cisco Discovery Protocol, a Cisco-proprietary Layer 2 protocol that advertises device identity, capabilities, and topology between directly connected Cisco gear, giving cyber tools a passive way to map network infrastructure. MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. chrome-devtools-mcp integration.
Exposes the Chrome DevTools Protocol (CDP) via the wss://api.cloudflare.com/client/v4/accounts/{ACCOUNT_ID}/browser-rendering/devtools/browser endpoint for CDP-compatible clients like Puppeteer and Playwright. Adds support for MCP clients through the chrome-devtools-mcp package, enabling tools like Claude Desktop and Cursor to use Browser Rendering as a remote browser.
2 details in Everything
Relaxed simultaneous connection limiting for Workers
Apr 9, 2026
· release notes
Cloudflare Workers now frees connection slots immediately after response headers arrive, eliminating spurious deadlock cancellations.
simultaneous open connections limit logic relaxed: a connection is freed as soon as response headers arrive rather than waiting for the full response body completion.
1 detail in Everything
Send CASB posture finding instances with webhooks
Apr 9, 2026
· release notes
Cloudflare One adds CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic.
Adds Integrations > Webhooks destination configuration for sending CASB posture finding instances to external systems Adds Flexible authentication options (None, Basic Auth, Bearer Auth, Static Headers, HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it. Adds Test delivery capability to send test requests before live sending Adds Send webhook action in the Cloud & SaaS SaaS Software delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally.
4 details in Everything
User risk scoring for high risk browsing activity
Apr 8, 2026
· release notes
Cloudflare One User Risk Scoring now incorporates Gateway DNS traffic patterns to elevate risk for high-risk browsing.
Incorporates direct signals from Gateway DNS traffic patterns into User Risk Scoring Adds Suspicious Security Domain Visited and High risk domain visited new risk behaviors in the dashboard
2 details in Everything
New Workers AI models for text generation and embedding in AI Search
Apr 8, 2026
· release notes
AI Search supports four new Workers AI models for text generation and embedding embedding Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG.
Adds @cf/zai-org/glm-4.7-flash model to AI Search with a 131,072 token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. Adds @cf/qwen/qwen3-30b-a3b-fp8 model to AI Search as a mixture-of-experts mixture-of-experts A model design that splits its layers into many expert sub-networks and routes each token to only a few. The model holds many parameters but spends the compute of a much smaller one per token. Adds @cf/qwen/qwen3-embedding-0.6b embedding model embedding model Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. Adds @cf/google/embeddinggemma-300m embedding model optimized for low-latency workloads
4 details in Everything
Website Source CSS content selectors for precise content extraction in AI Search
Apr 8, 2026
· release notes
AI Search now supports CSS content selectors for precise website crawling via API or dashboard.
└──▷ TRY IT
Extract only the main body text from blog posts while ignoring navigation and footers during AI Search indexing.
copy
$ curl "https://api.cloudflare.com/client/v4/accounts/{account_id}/ai-search/instances" \
-H "Authorization: Bearer {api_token}" \
-H "Content-Type: application/json" \
-d '{
"id": "my-ai-search",
"source": "https://example.com",
"type": "web-crawler",
"source_params": {
"web_crawler": {
"parse_options": {
"content_selector": [
{
"path": "**/blog/**",
"selector": "article .post-body"
}
]
}
}
}
}'
Adds source_params.web_crawler.parse_options.content_selector array to AI Search instance configuration, enabling CSS selector rules with URL glob patterns (up to 10 entries) for precise content extraction during web crawling.
1 detail in Everything
Manage mTLS and BYO CA certificates from the Cloudflare dashboard
Apr 7, 2026
· release notes
Cloudflare dashboard now supports managing mTLS mTLS Mutual TLS, an encrypted connection where both client and server present certificates to prove their identity. It helps services verify who they are communicating with.
Adds AOP certificate management in the Cloudflare dashboard to upload and manage own certificate authorities for Authenticated Origin Pulls directly from the UI Adds BYO Client mTLS certificate management in the Cloudflare dashboard to upload and manage own CA certificates for client mTLS enforcement without needing API access Adds CDN hostname to client mTLS certificate mapping in the Cloudflare dashboard to associate client mTLS certificates with specific hostnames directly from the UI
3 details in Everything
User Submission Triage Status Tracking
Apr 7, 2026
· release notes
Cloudflare Email security adds Triage Status Tracking for User Submissions with Unreviewed/Reviewed/Escalated states.
Status column added to the User Submissions table in the Cloudflare One dashboard, showing Unreviewed , Reviewed , or Escalated states for user-submitted emailsNew UI filtering capability allows SOC SOC A security operations center, the team or function that monitors threats, investigates alerts and coordinates incident response. Its work can be internal, outsourced or shared. Status column values
2 details in Everything
WebSockets now automatically reply to Close frames
Apr 7, 2026
· release notes
Cloudflare Workers now auto-reply WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output. allowHalfOpen flag for proxying control.
The Workers runtime now automatically sends a reciprocal Close frame when it receives a Close frame from the peer, matching the WebSocket specification. Adds allowHalfOpen: true option to WebSocketPair.accept() to enable half-open mode for independent close coordination in proxy scenarios.
2 details in Everything
Link aggregation (LACP) support for Cloudflare One Appliance
Apr 7, 2026
· release notes
Cloudflare One Appliance adds LACP support for bundling up to six LAN ports into a single logical interface.
Adds Link Aggregation Control Protocol (LACP) support on Cloudflare One Appliance to bundle up to six physical LAN ports.
1 detail in Everything
Organizations is now in public beta for enterprises
Apr 6, 2026
· release notes
Cloudflare Organizations public beta enables centralized multi-account management via new dashboard container and Terraform provider support
Adds a new Organizations top-level container for centrally managing multiple accounts, members, analytics, and shared policies from one location. Enables self-serve onboarding where enterprise customers can create an Organization in the dashboard and assign accounts where they are Super Administrators. Introduces Terraform provider support to provision Organizations, assign accounts, and configure settings programmatically via infrastructure as code.
3 details in Everything
Cloudflare Email Security adds automatic DANE support for MX deployments.
Regional MX hostnames now publish DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit. DANE verification is automatically enabled for all Advantage, Enterprise, and Enterprise + PhishGuard customers using regional MX deployments without additional configuration.
2 details in Everything
New ResponseTimeMs field in Gateway DNS Logpush dataset
Apr 6, 2026
· release notes
Adds ResponseTimeMs field to Gateway DNS Logpush dataset for latency analysis.
Control where your Containers run with regional and jurisdictional placement
Apr 5, 2026
· release notes
Cloudflare Containers adds regional and jurisdictional placement constraints
Adds regions constraint to control geographic placement for Cloudflare Containers (ENAM, WNAM, EEUR, WEUR) Adds jurisdiction constraint to restrict containers to compliance boundaries (eu, fedramp)
2 details in Everything
Google Gemma 4 26B A4B now available on Workers AI
Apr 4, 2026
· release notes
Google Gemma 4 26B A4B now available on Workers AI with vision, function calling function calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions.
Adds @cf/google/gemma-4-26b-a4b-it model to Workers AI
1 detail in Everything
Automatically retry on upstream provider failures on AI Gateway
Apr 2, 2026
· release notes
AI Gateway adds configurable automatic retry for upstream provider failures with delay and backoff settings.
Adds retry.max_attempts to AI Gateway configuration, supporting up to 5 attempts Adds retry.delay_min_ms and retry.delay_max_ms to control the interval between retries (100ms–5s) Adds retry.backoff_type with options Constant , Linear , or Exponential for the retry strategy
3 details in Everything
Session management for MCP server portals
Apr 2, 2026
· release notes
Adds in-session server management and reauthentication for MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Enables managing upstream MCP server connections directly within the client session without leaving the AI agent interface. Allows enabling or disabling specific upstream servers to toggle their tools on or off and reduce context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. Provides an authorization URL via MCP elicitation for reauthentication or changing data access permissions. Supports inline server management by asking the AI agent directly (e.g., "enable the wiki server").
4 details in Everything
Cloudflare Logpush adds native BigQuery BigQuery A serverless, cloud-hosted analytical database from Google that runs SQL queries across massive datasets without managing infrastructure, giving cyber tools scalable storage and fast querying over large volumes of log or event data.
Cloudflare Logs UI gets field filtering, custom columns, detail views and a toggle to the classic view.
Adds Filter by field capability to Cloudflare Access authentication logs and Gateway activity logs (DNS, Network, HTTP) allowing selection of any field value to narrow results Enables Customizable fields in the log table so users choose which fields to display, improving loading performance by querying fewer fields Adds ability to View details by selecting a timestamp to see full log entry information Introduces Switch to classic view option to return to the previous log viewer interface
4 details in Everything
New L4 transport telemetry fields in Workers
Apr 1, 2026
· release notes
Adds clientTcpRtt, clientQuicRtt, and edgeL4 properties to request.cf in Workers for L4 transport telemetry
Adds clientTcpRtt property on request.cf exposing smoothed TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. Adds clientQuicRtt property on request.cf exposing smoothed QUIC QUIC A UDP-based transport protocol standardized by the IETF that bakes in TLS 1.3, multiplexed streams, and connection migration, giving tools low-latency encrypted transport without head-of-line blocking. Adds edgeL4.deliveryRate property on request.cf exposing Layer 4 data delivery rate estimate in bytes per second
3 details in Everything
All Wrangler commands for Workflows now support local development
Apr 1, 2026
· release notes
Wrangler workflows commands support local development via --local and --port flags
└──▷ USE IT
List all workflow instances running in your local development environment.
shell
copy
npx wrangler workflows instances list my-workflow --local
Adds --local flag to all wrangler workflows commands to target a Workflow running in a local wrangler dev session instead of the production API. Adds --port argument to wrangler workflows commands to target a specific wrangler dev session (defaults to 8787). Enables full Workflow lifecycle management locally, including triggering, listing instances, pausing, resuming, restarting, terminating, and sending events via the new local flags.
3 details in Everything
Create, manage, search AI Search instances with Wrangler CLI
Apr 1, 2026
· release notes
Wrangler CLI gains ai-search subcommand namespace for managing and searching AI Search instances
└──▷ USE IT
Create a new AI Search instance backed by an R2 bucket named my-bucket non-interactively.
shell
copy
wrangler ai-search create my-instance --type r2 --source my-bucket
List all AI Search instances in the current account.
shell
copy
wrangler ai-search list
wrangler ai-search create creates a new AI Search instance, with an interactive wizard or flags like --type r2.wrangler ai-search list lists all AI Search instances in your account.wrangler ai-search get retrieves details for a specific AI Search instance.wrangler ai-search update updates the configuration of an existing AI Search instance.wrangler ai-search delete removes an AI Search instance.
+3 more
show less
wrangler ai-search search runs a query against an AI Search instance directly from the CLI.wrangler ai-search stats retrieves usage statistics for an AI Search instance.All wrangler ai-search * commands support the --json flag for structured output structured output Forcing a model's response to match a given format or JSON schema, so software can parse it reliably instead of hoping the text is well formed.
8 details in Everything
Routing Section Expansion on Cloudflare Radar
Apr 1, 2026
· release notes
Cloudflare Radar Routing section split into Overview, RPKI, Anomalies sub-pages with new Top 100 ASes table and RPKI validation views.
Adds Top 100 ASes ranking table to the Routing overview, sortable by customer cone size, IPv4 address space, or IPv6 IPv6 The current version of the Internet Protocol, standardized by the IETF, using 128-bit addresses to replace the exhausted IPv4 space. Cyber tools target it because modern networks run dual-stack or IPv6-only. Adds RPKI validation view on per-ASN ASN Autonomous System Number — a globally unique identifier assigned by regional internet registries to a network operator, letting routing protocols distinguish which organization controls a block of IP addresses. Improves IP address space chart to display both IPv4 and IPv6 trends stacked vertically across global, country, and AS views
3 details in Everything
New QUIC RTT and delivery rate fields
Apr 1, 2026
· release notes
New cf.timings.client_quic_rtt_msec and cf.edge.l4.delivery_rate fields in Cloudflare rules for transport-aware routing.
└──▷ USE IT
Tag high-latency connections (TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. QUIC QUIC A UDP-based transport protocol standardized by the IETF that bakes in TLS 1.3, multiplexed streams, and connection migration, giving tools low-latency encrypted transport without head-of-line blocking.
text
copy
cf.timings.client_tcp_rtt_msec > 200 or cf.timings.client_quic_rtt_msec > 200
Identify low-bandwidth client connections using the new delivery rate field.
text
copy
cf.edge.l4.delivery_rate > 0 and cf.edge.l4.delivery_rate < 100000
cf.timings.client_quic_rtt_msec field added to rule expressions for QUIC connection quality monitoringcf.edge.l4.delivery_rate field added to rule expressions for client bandwidth estimation
2 details in Everything
Deploy Hooks are now available for Workers Builds
Apr 1, 2026
· release notes
Cloudflare Workers Builds now supports Deploy Hooks to trigger builds via HTTP POST.
└──▷ USE IT
Trigger a Workers build via HTTP POST from an external system like a headless CMS CMS A web content management system for creating and managing digital content without writing code directly; cyber tools use CMS platforms to host documentation, portals, or reporting dashboards quickly.
shell
copy
curl -X POST "https://api.cloudflare.com/client/v4/workers/builds/deploy_hooks/<DEPLOY_HOOK_ID>"
Navigate the Cloudflare dashboard to create a new Deploy Hook URL.
📍 Workers & Pages › your Worker › Settings › Builds › Deploy Hooks
Adds the Deploy Hooks configuration page under Workers & Pages > Settings > Builds > Deploy Hooks to create unique URLs that trigger a Worker build and deploy on POST. Exposes the new API endpoint POST /client/v4/workers/builds/deploy_hooks/<DEPLOY_HOOK_ID> for triggering builds from headless CMS, Cron Triggers, or Slack bots. Adds automatic deduplication of redundant builds triggered by rapid webhook retries or CMS event bursts.
3 details in Everything
Cloudflare Internal DNS enters open beta for Enterprise Zero Trust and Gateway customers.
New RFC 9440 mTLS certificate fields in Workers
Mar 27, 2026
· release notes
Cloudflare Workers adds RFC 9440 mTLS mTLS Mutual TLS, an encrypted connection where both client and server present certificates to prove their identity. It helps services verify who they are communicating with. request.cf.tlsClientAuth
Adds certRFC9440, certRFC9440TooLarge, certChainRFC9440, and certChainRFC9440TooLarge fields to the request.cf.tlsClientAuth object in Cloudflare Workers for direct access to client certificates in RFC 9440 format Enables forwarding of mTLS client certificates to origin servers without custom parsing logic using the new RFC 9440 fields
2 details in Everything
Cloudflare adds Code Mode for MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
└──▷ TRY IT
Connect an MCP client using Code Mode.
copy
$ https://<subdomain>.<domain>/mcp?codemode=search_and_execute
Adds Code Mode toggle in Access controls > AI controls to disable the default behavior on MCP server portals Exposes a single code tool on MCP portals instead of individual upstream tools when Code Mode is active Supports ?codemode=search_and_execute query parameter on portal URLs for MCP client connections Runs generated code in an isolated Dynamic Worker environment to keep credentials out of model context
4 details in Everything
Context optimization for MCP server portals
Mar 26, 2026
· release notes
Adds optimize_context query parameter to MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds minimize_tools context optimization mode via the optimize_context query parameter to strip tool descriptions and schemas from the initial context payload. Adds search_and_execute context optimization mode via the optimize_context query parameter to expose only query and execute tools, reducing initial token cost.
2 details in Everything
Easily connect Containers and Sandboxes to Workers
Mar 26, 2026
· release notes
Outbound Workers let Containers and Sandboxes connect directly to other Workers functions and bindings via HTTP handlers.
Adds outbound handler to Sandbox and Container classes for capturing all HTTP requests from the container/sandbox Adds outboundByHost map on Sandbox/Container classes to route specific hostnames/IPs to distinct Worker functions Allows containers/sandboxes to access KV, R2, and Durable Object bindings via standard HTTP calls to named outbound Workers
3 details in Everything
URL Scanner improvements on Cloudflare Radar
Mar 26, 2026
· release notes
Cloudflare Radar URL Scanner adds live screenshots via Browser Rendering API, PDF/JSON export, and detailed file/IP data.
Live screenshots via Browser Rendering API in the summary cardSave as PDF button for print-optimized report aggregationDownload as JSON endpoint for raw scan data programmatic accessDetailed IP address data in the Network tab
4 details in Everything
Streaming ZIP file scanning removes per-file size limits
Mar 26, 2026
· release notes
DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
DLP scanning for ZIP files uses a streaming handler that scans contents element-by-element as data arrives Microsoft Office documents (DOCX, XLSX, PPTX) now benefit from the same streaming memory efficiency improvements
2 details in Everything
Access Durable Object jurisdiction via `ctx.id.jurisdiction`
Mar 26, 2026
· release notes
Durable Objects now expose ctx.id.jurisdiction for region-aware logic
Adds ctx.id.jurisdiction access inside Durable Object classes to report the creation jurisdiction (e.g., eu ) without passing arguments or persisting state
1 detail in Everything
Declare required secrets in your Wrangler configuration
Mar 25, 2026
· release notes
Wrangler adds secrets.required config to declare and validate Worker secrets
Adds secrets.required configuration property to Wrangler for declaring required Worker secrets wrangler dev and vite dev load only keys listed in secrets.required from .dev.vars or .envwrangler types generates typed bindings from secrets.required instead of inferring names from env fileswrangler deploy and wrangler versions upload validate that all secrets in secrets.required are configured on the Worker
4 details in Everything
└──▷ BREAKING ON UPGRADE
! wrangler dev and vite dev load only keys listed in secrets.required from .dev.vars or .env, excluding additional keys if secrets is defined! wrangler deploy and wrangler versions upload fail with an error listing which secrets need to be set if any required secrets are missing
Cloudflare Gateway adds Unsanitized HAR HAR An HTTP Archive file, a JSON-format log of all network requests and responses captured by a browser's developer tools, used by cyber tools to replay, inspect, or analyze web traffic without re-running a live session. DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Adds the Unsanitized HAR predefined DLP profile to detect HAR files in HTTP traffic Enables Gateway Redirect action to send users to https://har-sanitizer.pages.dev/ for sanitization Logs now classify detected HAR files as Unsanitized or Sanitized in Gateway logs
3 details in Everything
Logpush adds millisecond and nanosecond timestamp formats via timestamp_format in output_options.
Adds rfc3339ms and rfc3339ns to the timestamp_format config key within output_options for granular log timestamps
1 detail in Everything
Cloudflare introduces Cache Response Rules to modify origin responses (Cache-Control, headers) before caching via Dashboard or Rulesets API.
Adds new Cache Response Rules phase to evaluate and modify origin responses before they are cached. Enables modifying Cache-Control directives such as no-store, max-age, and s-maxage on origin responses. Allows setting a different browser Cache-Control header independent of internal Cloudflare caching logic. Supports adding, setting, or removing cache tags via the Cache-Tag header, including format conversion from other CDNs. Permits stripping blocking headers like Set-Cookie , ETag , and Last-Modified to force caching of previously uncacheable content.
5 details in Everything
OIDC Claims filtering now available in Gateway Firewall, Resolver, and Egress policies
Mar 24, 2026
· release notes
Cloudflare Gateway expands policy capabilities by introducing OIDC OIDC OpenID Connect, a sign-in protocol built on OAuth 2.0. An application uses identity information from a trusted provider instead of maintaining a separate password for each user.
Adds OIDC Claims selector to Firewall, Resolver, and Egress policy builders
1 detail in Everything
Advanced WAF customization for AI Crawl Control blocks
Mar 24, 2026
· release notes
AI Crawl Control now preserves custom WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Custom modifications to the underlying WAF rule are preserved when updating crawler actions in AI Crawl Control.
1 detail in Everything
Dynamic Workers open beta introduces runtime code execution via env.LOADER.load() and new helper libraries for agents
Adds env.LOADER.load() method to spin up new Workers at runtime with specified compatibilityDate, mainModule, modules, and globalOutbound settings Adds worker.getEntrypoint() .fetch(request) API to invoke the newly spawned Dynamic Worker Adds get(id, callback) mode to cache and reuse Dynamic Workers by ID for subsequent requests Introduces @cloudflare/codemode library with a code() tool to replace multiple LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code. Introduces @cloudflare/worker-bundler library to resolve npm dependencies and bundle source files at runtime
+1 more
show less
Introduces @cloudflare/shell library providing a virtual filesystem backed by SQLite and R2
6 details in Everything
Web Assets fields now available in GraphQL Analytics API
Mar 23, 2026
· release notes
Web Assets fields added to GraphQL Analytics API for request-level operation and label visibility
Adds webAssetsOperationId field to httpRequestsAdaptive dataset to expose the saved endpoint ID matched by a request. Adds webAssetsLabelsManaged field to httpRequestsAdaptiveGroups dataset to expose managed labels (e.g., cf-llm, cf-log-in) mapped to the matched operation.
2 details in Everything
Agents SDK v0.8.0: readable state, idempotent schedules, typed AgentClient, and Zod 4
Mar 23, 2026
· release notes
Agents SDK v0.8.0 adds readable state, idempotent schedules, typed AgentClient, and Zod 4 support.
useAgent and AgentClient now expose a reactive state property for direct state access.schedule() supports an idempotent option to deduplicate schedule rows across Durable Object restarts.AgentClient accepts an optional agent type parameter for full TypeScript inference on RPC RPC Remote Procedure Call, a protocol that lets a program execute a function on another machine as if it were local, giving cyber tools a structured way to communicate across processes or hosts without managing raw sockets.
3 details in Everything
└──▷ BREAKING ON UPGRADE
! Zod v3 is no longer supported; agents, @cloudflare/ai-chat, and @cloudflare/codemode now require Zod ^4.0.0.
AI Search UI snippets and MCP support
Mar 23, 2026
· release notes
AI Search gains public endpoints, embeddable UI snippets, and MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds Public Endpoint toggle in AI Search Settings to expose search without API auth. Adds UI snippets (search modal component) configurable at search.ai.cloudflare.com for website embedding embedding Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. Adds MCP endpoint at https://<PUBLIC_ENDPOINT_ID>.search.ai.cloudflare.com/mcp for agent integration.
3 details in Everything
Custom metadata filtering for AI Search
Mar 23, 2026
· release notes
Custom metadata filtering for AI Search allows defining fields and filtering by them.
Adds custom_metadata field to AI Search instance configuration for defining up to 5 custom fields Enables filtering search results by custom metadata fields using the filters object in ai_search_options
2 details in Everything
R2 SQL now supports over 190 new functions, expressions, and complex types
Mar 23, 2026
· release notes
R2 SQL adds CASE expressions, CTEs, complex types, and 190+ new functions.
Adds support for CASE expressions (searched and simple forms) enabling conditional logic directly in SQL queries Adds Common Table Expressions (CTEs) via the WITH ... AS syntax with support for chained CTEs referencing a single table Adds full struct/array/map access allowing query of struct fields with bracket notation, 46 array functions, and map key/value extraction Adds EXPLAIN, column aliases in all clauses, arithmetic in clauses, and EXTRACT in SELECT/WHERE/GROUP BY/HAVING/ORDER BY Adds CAST, TRY_CAST, and :: shorthand for type casting, plus 163 scalar and 33 aggregate functions including statistical and bitwise operations
5 details in Everything
Workflow instances now support pause(), resume(), restart(), and terminate() methods in local development
Mar 23, 2026
· release notes
Cloudflare Workflow instances support pause() , resume() , restart() , and terminate() methods in local dev
New AI Search REST API endpoints for /search and /chat/completions
Mar 23, 2026
· release notes
Cloudflare AI Search adds OpenAI-compatible /search and /chat/completions REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Adds POST /accounts/{account_id}/ai-search/instances/{name}/chat/completions endpoint for chat completions using an OpenAI-compatible messages array format. Adds POST /accounts/{account_id}/ai-search/instances/{name}/search endpoint for AI Search queries.
2 details in Everything
Observability for Workers VPC Services
Mar 20, 2026
· release notes
New Metrics and Settings tabs for Workers VPC VPC A logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware.
Adds a Metrics tab to each VPC Service in the Cloudflare dashboard to monitor connection health and debug failures.
1 detail in Everything
Cloudflare Access adds Managed OAuth for non-browser clients via API and UI
Enables oauth_configuration.enabled on the Access applications API endpoint to activate Managed OAuth transport. Adds Managed OAuth toggle under Advanced settings in the Zero Trust > Access controls > Applications UI.
2 details in Everything
Stream logs from multiple replicas of Cloudflare Tunnel simultaneously
Mar 20, 2026
· release notes
Cloudflare Tunnel now supports streaming logs from multiple replicas simultaneously in the Cloudflare One dashboard.
Route MCP server portal traffic through Cloudflare Gateway
Mar 20, 2026
· release notes
MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
DNS Analytics for Customer Metadata Boundary set to EU region
Mar 20, 2026
· release notes
DNS Analytics for Customer Metadata Boundary set to EU region
Enables DNS Analytics access and queries for zones in accounts with CMB=EU, storing and querying data within the EU region.
1 detail in Everything
Manage Cloudflare Tunnels with Wrangler
Mar 19, 2026
· release notes
Wrangler adds wrangler tunnel subcommands to manage Cloudflare Tunnels from the CLI
Adds wrangler tunnel quick-start command to start a temporary tunnel without an account using Quick Tunnels. Automatically downloads and manages the cloudflared binary on first use of any wrangler tunnel command.
2 details in Everything
Moonshot AI Kimi K2.5 now available on Workers AI
Mar 19, 2026
· release notes
Moonshot AI Kimi K2.5 now available on Workers AI with multi-turn tool calling tool calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions.
Adds @cf/moonshotai/kimi-k2.5 model to Workers AI inference platform Adds support for 256k context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. Adds multi-turn tool calling capability to Kimi K2.5 Adds vision input support (images alongside text) to Kimi K2.5 Adds structured outputs structured outputs Forcing a model's response to match a given format or JSON schema, so software can parse it reliably instead of hoping the text is well formed. JSON mode JSON mode Forcing a model's response to match a given format or JSON schema, so software can parse it reliably instead of hoping the text is well formed.
+3 more
show less
Adds function calling function calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions. Surfaces cached tokens as a usage metric and offers pricing discount on cached tokens Redesigns asynchronous batch API with pull-based system for processing queued requests
8 details in Everything
Hyperdrive now supports custom TLS/SSL certificates for MySQL
Mar 19, 2026
· release notes
Hyperdrive now supports custom TLS/SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination. mTLS mTLS Mutual TLS, an encrypted connection where both client and server present certificates to prove their identity. It helps services verify who they are communicating with.
└──▷ USE IT
Upload a CA certificate that your MySQL database server uses, so Hyperdrive can verify it.
shell
copy
npx wrangler cert upload certificate-authority --ca-cert your-ca-cert.pem --name your-custom-ca-name
Adds npx wrangler cert upload certificate-authority command to upload a CA certificate for Hyperdrive use Adds --ca-certificate-id and --sslmode arguments to npx wrangler hyperdrive create to configure MySQL TLS settings Enables client certificate (mTLS) authentication for Hyperdrive connections to MySQL databases
3 details in Everything
Cloudflare SCIM SCIM A standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave.
Logs specific SCIM actions: Create/Update/Replace/Delete SCIM User and Create/Update/Delete SCIM Group.
1 detail in Everything
Worker execution timing field now available in Rules
Mar 18, 2026
· release notes
Cloudflare Ruleset Engine adds cf.timings.worker_msec field for Worker latency monitoring
New real-time logo match preview in Cloudflare Security Center Brand Protection dashboard allows fine-tuning similarity scores before saving.
Adds Logo Match Preview to the Brand Protection dashboard for visual assets Allows adjusting similarity score from 75% to 100% with real-time result refresh during logo upload Enables review of specific triggered logos before finalizing brand detection query
3 details in Everything
SCIM provisioning for Authentik is now Generally Available
Mar 18, 2026
· release notes
Cloudflare dashboard adds SCIM SCIM A standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave. identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems.
Enables syncing users and group information from Authentik to Cloudflare via SCIM
1 detail in Everything
Media Transformations binding for Workers
Mar 18, 2026
· release notes
New media binding for Workers enables video transform capabilities directly in code
Adds the media configuration key to Wrangler config files (e.g., wrangler.toml) to bind Media Transformations resources Introduces the env.MEDIA.input() method as the entry point for processing video streams within Workers Supports chaining .transform() with width/height parameters and .output() specifying modes: video, frame, spritesheet, or audio
3 details in Everything
New Security Overview UI adds criticality ratings, detection tools section, and industry peer comparisons for Enterprise customers.
Adds Criticality rating to all Security Insights to prioritize high-impact actions Adds new Detection Tools Section in the Security Overview to view enabled and activatable security detectors Adds Industry Peer Comparison module to Security Reports for Enterprise customers to benchmark security posture against industry peers
3 details in Everything
Log AI Gateway request metadata without storing payloads
Mar 17, 2026
· release notes
Adds cf-aig-collect-log-payload header to AI Gateway for logging metadata without storing request/response bodies
New cf-aig-collect-log-payload HTTP header on the https://gateway.ai.cloudflare.com/v1/$ACCOUNT_ID/$GATEWAY_ID/openai/chat/completions endpoint lets you skip payload storage while keeping metadata logs like token counts and cost. Default behavior for the new cf-aig-collect-log-payload header is true, storing payloads; setting it to false excludes sensitive data from logs.
2 details in Everything
@cloudflare/codemode v0.2.1: MCP barrel export, zero-dependency main entry point, and custom sandbox modules
Mar 17, 2026
· release notes
@cloudflare/codemode v0.2.1 adds MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
@cloudflare/codemode/mcp exports codeMcpServer() to wrap an existing MCP server and openApiMcpServer() to create search/execute tools from an OpenAPI OpenAPI A vendor-neutral specification for describing REST APIs in a machine-readable format, maintained by the OpenAPI Initiative. Cyber tools use it to auto-generate clients, documentation, and validation from a single source of truth. The main entry point @cloudflare/codemode no longer requires ai or zod as peer dependencies. DynamicWorkerExecutor accepts an optional modules option to inject custom ES modules into the sandbox.
3 details in Everything
└──▷ BREAKING ON UPGRADE
! generateTypes and the ToolDescriptor / ToolDescriptors types have moved to @cloudflare/codemode/ai.
Return up to 50 query results with values or metadata
Mar 16, 2026
· release notes
Cloudflare Vectorize topK limit increased to 50 for query results
The topK parameter in Vectorize queries now supports a maximum value of 50, up from the previous limit of 20. The higher topK limit applies to queries using returnValues: true or returnMetadata: "all".
2 details in Everything
Unlimited result paging in Investigations
Mar 15, 2026
· release notes
Unlimited result paging in Investigations dashboard and API for Email Security
Removes the previous 1,000-record cap in the Investigations UI dashboard, allowing navigation through complete result sets. Increases Investigations API page size to 10,000 records per page (up from 1,000) and removes the total result volume cap.
2 details in Everything
Access Durable Object name via `ctx.id.name`
Mar 15, 2026
· release notes
Workers runtime exposes ctx.id.name in Durable Objects to retrieve the access name without passing it explicitly.
Adds ctx.id.name to Durable Object context to expose the name used when accessed via idFromName() or getByName()
1 detail in Everything
SSH into running Container instances
Mar 12, 2026
· release notes
Wrangler adds wrangler containers ssh command and wrangler_ssh config keys for direct SSH access to Containers.
Adds the wrangler containers ssh <INSTANCE_ID> subcommand to open an interactive SSH session or execute single commands in a running Container instance Adds the wrangler_ssh.enabled configuration key (supporting both JSON and TOML formats) to enable SSH access for a specific Container Adds the authorized_keys configuration array to specify the public keys permitted for authentication within the Container
3 details in Everything
Retry-After HTTP header for retryable 1xxx errors
Mar 12, 2026
· release notes
Cloudflare adds Retry-After HTTP header to retryable 1xxx errors for faster client recovery
└──▷ USE IT
Verify that the Retry-After header is present on a rate-limited response to configure client-side wait logic.
shell
copy
curl -s --compressed -D - -o /dev/null -H "Accept: application/json" -A "TestAgent/1.0" -H "Accept-Encoding: gzip, deflate" "<YOUR_DOMAIN>/cdn-cgi/error/1015" | grep -i retry-after
Adds Retry-After header to Cloudflare-generated 1xxx error responses (1004, 1005, 1015, 1033, 1038, 1200, 1205) for standard client retry behavior
1 detail in Everything
List Container instances with `wrangler containers instances`
Mar 12, 2026
· release notes
Wrangler adds wrangler containers instances command to list container app instances from CLI
Adds wrangler containers instances <APPLICATION_ID> subcommand to list Container application instances (ID, name, state, location, version, creation time) Supports --json flag for machine-readable output in the wrangler containers instances command
2 details in Everything
JSON responses and RFC 9457 support for Cloudflare 1xxx errors
Mar 11, 2026
· release notes
Cloudflare 1xxx errors now return structured JSON following RFC 9457 when clients send Accept: application/json or Accept: application/problem+json.
└──▷ TRY IT
Parse structured error details from Cloudflare's RFC 9457 compliant responses for programmatic handling
copy
$ curl -s --compressed -H "Accept: application/problem+json" -A "TestAgent/1.0" -H "Accept-Encoding: gzip, deflate" "<YOUR_DOMAIN>/cdn-cgi/error/1015" | jq .
Accept: application/problem+json now returns RFC 9457 compliant Problem Details JSON for Cloudflare-generated 1xxx errorshttp_status field renamed to status in JSON and Markdown frontmatter responses for 1xxx errorswhat_happened field renamed to detail in JSON-only responses for 1xxx errors
3 details in Everything
NVIDIA Nemotron 3 Super now available on Workers AI
Mar 11, 2026
· release notes
NVIDIA Nemotron 3 Super now available on Workers AI via @cf/nvidia/nemotron-3-120b-a12b
Adds @cf/nvidia/nemotron-3-120b-a12b model to Workers AI for reasoning and tool calling tool calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions.
1 detail in Everything
Ingest field selection for Log Explorer
Mar 11, 2026
· release notes
Cloudflare Log Explorer adds ingest field selection via API and UI
Adds fields array to Log Explorer dataset configuration to specify exactly which data fields are ingested. Enables dynamic updates of the fields list for existing, already enabled logstreams.
2 details in Everything
WARP client for Windows (version 2026.3.566.1)
Mar 10, 2026
· release notes
WARP Windows beta gets Cloudflare One UI with connectivity button and collapsible nav, plus QUIC QUIC A UDP-based transport protocol standardized by the IETF that bakes in TLS 1.3, multiplexed streams, and connection migration, giving tools low-latency encrypted transport without head-of-line blocking.
Introduces the new Cloudflare One Client interface for Windows, changing connectivity management from a toggle to a button and adding a collapsible navigation bar for settings and device profile access Adds detailed QUIC connection metrics to diagnostic logs for improved troubleshooting Switches tunnel congestion control algorithm to Cubic for improved reliability across platforms
3 details in Everything
Audit logs (version 2) - General Availability
Mar 10, 2026
· release notes
Cloudflare Audit Logs v2 GA with standardized format and new API endpoint.
Audit Logs v2 is now generally available across ~95% of products Supports granular filtering with over 20 parameters including actor, action type, and resource
2 details in Everything
Crawl entire websites with a single API call using Browser Rendering
Mar 10, 2026
· release notes
Cloudflare adds /crawl API endpoint for full-website crawling with browser rendering
└──▷ TRY IT
Check the status of a previous crawl job using the returned job ID
copy
$ curl -X GET 'https://api.cloudflare.com/client/v4/accounts/{account_id}/browser-rendering/crawl/{job_id}' \
-H 'Authorization: Bearer <apiToken>'
Adds POST /client/v4/accounts/{account_id}/browser-rendering/crawl endpoint to initiate asynchronous website crawls Adds GET /client/v4/accounts/{account_id}/browser-rendering/crawl/{job_id} endpoint to retrieve crawl results Enables structured JSON output format powered by Workers AI for crawled content Supports render: false parameter in crawl request body to enable static HTML mode
4 details in Everything
WARP client for macOS (version 2026.3.566.1)
Mar 10, 2026
· release notes
Cloudflare WARP for macOS 2026.3.566.1 adds new UI with connectivity button, collapsible nav, and tunnel stats monitoring
Redesigned client interface changes connectivity management from a toggle to a button New collapsible navigation bar in the expanded view exposes connectivity, settings, and device profile information Added detailed QUIC QUIC A UDP-based transport protocol standardized by the IETF that bakes in TLS 1.3, multiplexed streams, and connection migration, giving tools low-latency encrypted transport without head-of-line blocking. Added monitoring for tunnel statistics collection timeouts
4 details in Everything
└──▷ BREAKING ON UPGRADE
! Empty MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies.
New Vulnerability Scanner for API Shield
Mar 9, 2026
· release notes
Cloudflare launches open beta Web and API Vulnerability Scanner for API Shield subscribers via API.
Introduces the Web and API Vulnerability Scanner (Open Beta) as a stateful DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces. Adds support for detecting Broken Object Level Authorization (BOLA BOLA Broken Object Level Authorization, an API vulnerability class where a server fails to verify that the requesting user owns or may access the object ID they supply, letting attackers read or modify other users' data.
2 details in Everything
New MCP Portal Logs dataset and new fields across multiple Logpush datasets in Cloudflare Logs
Mar 9, 2026
· release notes
New MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds the MCP Portal Logs dataset to Logpush with fields including ClientCountry, ClientIP, ToolCallName, SessionID, and ServerResponseDurationMs for tracking Model Context Protocol Model Context Protocol Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Adds HTTPResponseBody and HTTPResponseHeaders fields to the DEX Application Tests Logpush dataset.
2 details in Everything
Region Filtering, AS Traffic Volume, and Navigation Improvements on Cloudflare Radar
Mar 6, 2026
· release notes
Cloudflare Radar adds region filtering to location-aware pages, AS traffic volume views, and breadcrumb navigation.
Adds region filtering (continents, subregions, political regions, US Census regions) to all location-aware pages on Cloudflare Radar Introduces a new traffic volume view showing top autonomous systems and countries/territories for a given location Adds AS and location dimensions to the Data Explorer for HTTP, DNS, and NetFlows datasets Enables breadcrumb navigation on most Cloudflare Radar pages
4 details in Everything
Workflow steps now expose retry attempt number via step context
Mar 6, 2026
· release notes
Cloudflare Workflows exposes retry attempt number in step context via ctx.attempt
Dismiss and filter matches in Brand Protection
Mar 6, 2026
· release notes
Brand Protection adds match dismissal and active/dismissed view toggle
Adds UI control to dismiss specific Brand Protection matches as benign or false positives Adds Show/Hide visibility toggle to switch between active matches and dismissed ones in the triage view
2 details in Everything
User risk score selector in Access policies
Mar 4, 2026
· release notes
Adds User Risk Score selector to Cloudflare Access policies for behavior-based access control.
New conversion options for Markdown Conversion
Mar 4, 2026
· release notes
Workers AI toMarkdown now accepts conversionOptions for HTML selectors, PDF metadata exclusion, and image description languages.
└──▷ TRY IT
Use the REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
copy
$ curl https://api.cloudflare.com/client/v4/accounts/{ACCOUNT_ID}/ai/tomarkdown \
-H 'Authorization: Bearer {API_TOKEN}' \
-F 'files=@index.html' \
-F 'conversionOptions={"html": {"cssSelector": "article.content"}}'
Adds conversionOptions.html.cssSelector to the Workers AI toMarkdown function to extract specific HTML content via CSS Adds conversionOptions.image.descriptionLanguage to specify the language for AI-generated image descriptions in Markdown output Adds conversionOptions.pdf.excludeMetadata to omit PDF metadata from the converted Markdown
3 details in Everything
Gateway Authorization Proxy and hosted PAC files (open beta)
Mar 4, 2026
· release notes
Cloudflare Gateway adds authorization proxy and hosted PAC PAC A Proxy Auto-Configuration file, a JavaScript snippet a browser or OS fetches to decide which proxy server to route each request through, letting cyber tools intercept or redirect traffic without per-app configuration.
└──▷ TRY IT
Host a PAC file for browser configuration.
copy
$ https://pac.cloudflare-gateway.com/<account-id>/<slug>
Adds Gateway Authorization Proxy to replace static IP-based authorization with Cloudflare Access authentication Adds ability to display multiple identity providers identity providers A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. Adds support for creating and hosting PAC files at https://pac.cloudflare-gateway.com/<account-id>/<slug>
3 details in Everything
Cloudflare Sandboxes adds real-time filesystem watching via sandbox.watch() and parseSSEStream.
sandbox.watch(path, options) returns a Server-Sent Events stream for create, modify, delete, and move events.@cloudflare/sandbox exports parseSSEStream to consume watch events server-side.
2 details in Everything
Network Quality Test on Cloudflare Radar
Mar 3, 2026
· release notes
New Radar page for network quality insights.
Workflows step limit increased to 25,000 steps per instance
Mar 3, 2026
· release notes
Cloudflare Workflows step limit raised from 1024 to configurable 25,000 via wrangler.jsonc
Increases the default maximum steps per Workflow instance from 1,024 to 10,000 on Workers Paid plans. Adds support for configuring a custom step limit up to 25,000 using the limits.steps key in wrangler.jsonc.
2 details in Everything
Get started with AI Gateway automatically
Mar 2, 2026
· release notes
Adds automatic default AI Gateway provisioning via /default gateway ID.
Copy Cloudflare One resources as JSON or POST requests
Mar 2, 2026
· release notes
Adds Copy as JSON and Copy as POST request options to Cloudflare One resource menus in the dashboard
Adds Copy as JSON menu option for supported Cloudflare One resources, outputting a minimal JSON representation of the resource's current fields. Adds Copy as POST request menu option for supported Cloudflare One resources, outputting a ready-to-use API POST request body. Initial support covers Access applications, Access policies, Gateway policies, Resolver policies, Service tokens, and Identity providers Identity providers A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems.
3 details in Everything
Agents SDK v0.7.0: Observability rewrite, keepAlive, and waitForMcpConnections
Mar 2, 2026
· release notes
Cloudflare Agents SDK v0.7.0 adds keepAlive, waitForMcpConnections, and structured observability
Adds keepAlive() and keepAliveWhile() methods to prevent Durable Object eviction during long-running work Adds waitForMcpConnections option to AIChatAgent to ensure MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Rewrites observability with structured events published to diagnostics_channels, exposed via the subscribe() helper from agents/observability
3 details in Everything
New protocols added for Gateway Protocol Detection (Beta)
Feb 27, 2026
· release notes
Cloudflare Gateway Protocol Detection (Beta) adds IMAP, POP3, SMTP SMTP The application-layer protocol used to send email between servers and from clients to servers; cyber tools use it to relay alerts, phishing simulations, or exfiltrated data over standard mail infrastructure. LDAP LDAP A protocol for querying and modifying directory services, standardized under RFC 4511, commonly used to look up users, groups, and attributes in corporate identity stores like Active Directory.
Adds IMAP detection for Gateway Protocol Detection to identify email retrieval traffic Adds POP3 detection for Gateway Protocol Detection to identify email retrieval traffic Adds SMTP detection for Gateway Protocol Detection to identify email sending traffic Adds MYSQL detection for Gateway Protocol Detection to identify database wire protocol traffic Adds RSYNC-DAEMON detection for Gateway Protocol Detection to identify rsync daemon protocol traffic
+2 more
show less
Adds LDAP detection for Gateway Protocol Detection to identify Lightweight Directory Access Protocol traffic Adds NTP detection for Gateway Protocol Detection to identify Network Time Protocol traffic
7 details in Everything
Export MCP server portal logs with Logpush
Feb 27, 2026
· release notes
MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. SIEM SIEM Security information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents.
Adds Logpush integration for MCP server portal activity logs
1 detail in Everything
Post-Quantum Encryption and Key Transparency on Cloudflare Radar
Feb 27, 2026
· release notes
Cloudflare Radar adds Post-Quantum Post-Quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA.
Adds GET /post_quantum/tls/support endpoint to test host post-quantum TLS key exchange support Adds GET /post_quantum/origin/summary/{dimension} endpoint to return origin PQ data by key agreement algorithm Adds GET /post_quantum/origin/timeseries_groups/{dimension} endpoint to return PQ timeseries data grouped by algorithm Adds Key Transparency section and Key Transparency Auditor API for monitoring WhatsApp and Facebook Messenger Transport logs
4 details in Everything
Markdown responses for Cloudflare 1xxx errors
Feb 26, 2026
· release notes
Cloudflare adds structured Markdown responses for 1xxx errors via Accept header negotiation.
No config? No problem. Just `wrangler deploy`
Feb 25, 2026
· release notes
Wrangler 4.68.0 GA autoconfig allows wrangler deploy without a pre-existing config file
wrangler deploy now automatically detects the framework from package.json, installs required adapters, and generates a wrangler.jsonc file when none exists
1 detail in Everything
Write structured queries to filter and search your Workers logs and traces
Feb 25, 2026
· release notes
Cloudflare Workers Observability gains a new structured query language enabling precise filtering of logs and traces via both text-based queries and a visual Query Builder.
RPKI ASPA Deployment Insights on Cloudflare Radar
Feb 25, 2026
· release notes
New RPKI ASPA deployment insights and API on Cloudflare Radar.
Adds /bgp/rpki/aspa/snapshot, /bgp/rpki/aspa/changes, and /bgp/rpki/aspa/timeseries API endpoints to retrieve ASPA objects, changes, and counts. Adds ASPA deployment trend widget on the global routing page counting daily ASPA objects. Adds searchable recent ASPA objects by ASN ASN Autonomous System Number — a globally unique identifier assigned by regional internet registries to a network operator, letting routing protocols distinguish which organization controls a block of IP addresses. Adds ASPA deployment rate widget for countries/regions on country and region routing pages. Adds checkmarks for ASPA-verified upstreams, a dedicated upstream table, and daily timeline on AS routing pages.
5 details in Everything
Agents SDK v0.6.0: RPC transport for MCP, optional OAuth, hardened schema conversion, and @cloudflare/ai-chat fixes
Feb 25, 2026
· release notes
Cloudflare Agents SDK v0.6.0 adds RPC RPC Remote Procedure Call, a protocol that lets a program execute a function on another machine as if it were local, giving cyber tools a structured way to communicate across processes or hosts without managing raw sockets. MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds addMcpServer support for passing a Durable Object namespace as the second parameter to connect an Agent to an McpAgent over RPC Makes OAuth optional for MCP connections by allowing addMcpServer to work without a callbackHost when authentication is not required Hardens the schema converter used by generateTypes() and getAITools() with support for tuple types, $ref resolution, and per-tool error isolation
3 details in Everything
deleteAll() now deletes Durable Object alarm
Feb 24, 2026
· release notes
deleteAll() for Durable Objects now purges alarms alongside stored data
Adds automatic alarm deletion to the deleteAll() Storage API method for Durable Objects with a compatibility date of 2026-02-24 or later
1 detail in Everything
Dropped event metrics, typed Pipelines bindings, and improved setup
Feb 24, 2026
· release notes
Cloudflare Pipelines adds typed bindings via wrangler types, dropped event metrics dashboard/GraphQL API, and simplified setup command.
└──▷ TRY IT
Generate TypeScript types for your stream to catch schema mismatches before deployment.
wrangler pipelines setup command with Simple mode automatically creates the R2 bucket, enables R2 Data Catalog, and applies recommended defaults for stream ingestion.wrangler types generates schema-specific TypeScript types for Pipeline bindings, allowing compile-time validation of fields like user_id or amount via interfaces such as EcommerceStreamRecord.New pipelinesUserErrorsAdaptiveGroups GraphQL dataset and queryable metrics surface dropped events with error types (missing_field, type_mismatch, etc.) to identify root causes.
3 details in Everything
WARP client for Windows (version 2026.1.150.0)
Feb 24, 2026
· release notes
WARP for Windows GA with NetBIOS control and multi-user registration fixes
Adds support for managing NetBIOS over TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it.
1 detail in Everything
Stream live inputs can now be disabled and enabled
Feb 24, 2026
· release notes
API and UI support for enabling/disabling Cloudflare Stream live inputs
Adds enabled property to the PUT /accounts/{account_id}/stream/live_inputs/{input_id} endpoint to control input state Adds ability to disable/enable live inputs from the Dashboard Live inputs list or detail page
2 details in Everything
Hyperdrive no longer caches queries using STABLE PostgreSQL functions
Feb 23, 2026
· release notes
Hyperdrive uncaches queries containing PostgreSQL STABLE functions like NOW() .
Treats queries containing PostgreSQL STABLE functions (e.g., NOW() ) as uncacheable. Updates text-based pattern matching to detect STABLE functions alongside existing VOLATILE detection.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! Queries using PostgreSQL STABLE functions such as NOW() are no longer cached, potentially increasing backend load if you relied on that caching.
Backup and restore API for Sandbox SDK
Feb 23, 2026
· release notes
Cloudflare Sandboxes adds createBackup() and restoreBackup() methods for point-in-time directory snapshots
Adds createBackup() method to Cloudflare Sandbox SDK for creating point-in-time snapshots of directories. Adds restoreBackup() method to Cloudflare Sandbox SDK for restoring previously created snapshots. Backups are stored in R2 and support TTLs via object lifecycle rules.
3 details in Everything
Saved views for Threat Events dashboard
@cloudflare/codemode v0.1.0: a new runtime agnostic modular architecture
Feb 20, 2026
· release notes
@cloudflare/codemode v0.1.0 introduces a modular SDK with createCodeTool() , Executor interface, and DynamicWorkerExecutor for runtime-agnostic code execution.
Exports createCodeTool() from the new import path @cloudflare/codemode/ai to return a standard AI SDK Tool for use in agents. Adds the Executor interface with an execute(code, fns) contract, allowing implementation of any code sandboxing sandboxing Running code inside a restricted environment that limits what it can access or change. The isolation reduces the impact of mistakes or untrusted code, depending on the sandbox's controls. Introduces DynamicWorkerExecutor to run generated code in a Dynamic Worker Loader, defaulting to network isolation where fetch() and connect() are blocked (globalOutbound: null). Configures execution timeout via the timeout option on DynamicWorkerExecutor, with a default of 30s. Captures console output by returning console.log/warn/error data in ExecuteResult.logs.
5 details in Everything
└──▷ BREAKING ON UPGRADE
! Removes the experimental_codemode() function and CodeModeProxy class, as the package no longer manages LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code. ! Changes the import path for createCodeTool() , which must now be imported from @cloudflare/codemode/ai instead of the previous location.
Understand CASB findings instantly with Cloudy Summaries
Feb 20, 2026
· release notes
Adds AI-generated Cloudy Summaries to CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic.
Integrates Cloudflare's Cloudy AI into CASB Posture Findings to generate plain-language summaries of security misconfigurations, third-party app risks, and data exposures
1 detail in Everything
Manage Cloudflare Tunnel directly from the main Cloudflare Dashboard
Feb 20, 2026
· release notes
Cloudflare Tunnel management added to main Dashboard Networking > Tunnels UI for lifecycle and routing.
AI dashboard experience improvements
Feb 19, 2026
· release notes
Cloudflare adds top-level AI dashboard section, OpenAI-compatible endpoint display for new gateways, and route name copying
Adds a top-level AI section to the Cloudflare dashboard sidebar to access AI features directly. Displays the gateway's OpenAI-compatible endpoint automatically in the first-run setup experience for AI Gateway. Enables copying route names to clipboard with a single click in the Dynamic Routing route builder. Combines previously separate code example sections into a unified view with dropdown selectors for API type, provider, SDK, and authentication method.
4 details in Everything
Cloudforce One Threat events graphs are now visible in the dashboard
Feb 19, 2026
· release notes
Cloudforce One adds Sankey diagrams and time-based distribution views to the Threat Events dashboard
Adds Sankey Diagrams to the Cloudforce One Threat Events dashboard for tracing attack flow from origin to target country. Adds Dataset Distribution over time visualization to pivot views for campaign scope analysis. Adds Enhanced Filtering capability directly within the threat event charts.
3 details in Everything
New cfWorker metric in Server-Timing header
Feb 18, 2026
· release notes
Adds cfWorker metric to Server-Timing header for precise Worker execution time debugging
Server-Timing header now includes a cfWorker metric that measures time spent executing Cloudflare Workers (including subrequests), excluding origin fetch time cfWorker metric is enabled by default when Real User Monitoring (RUM RUM Real User Monitoring — a technique that collects performance and behaviour data from actual users' browsers or clients in production, giving cyber tools visibility into real-world latency and errors rather than synthetic test results.
2 details in Everything
Streamlined clientless browser isolation for private applications
Feb 17, 2026
· release notes
Adds Allow clientless access toggle to private self-hosted applications in Cloudflare Access.
Allows enabling clientless browser isolation directly within a private self-hosted application via the new Allow clientless access setting.
1 detail in Everything
Agents SDK v0.5.0: Protocol message control, retry utilities, data parts, and @cloudflare/ai-chat v0.1.0
Feb 17, 2026
· release notes
Agents SDK v0.5.0 adds this.retry() with per-task config, shouldSendProtocolMessages hook, and @cloudflare/ai-chat v0.1.0
Adds this.retry() method for async operations with exponential backoff, jitter, and optional shouldRetry predicate to control retry logic. Enables per-task retry configuration via the retry option in schedule() , scheduleEvery() , and addMcpServer() calls, persisted in SQLite alongside the task. Introduces class-level retry defaults via static options = { retry: { maxAttempts: N } } on Agent subclasses. Adds shouldSendProtocolMessages(connection, ctx) hook to suppress JSON protocol frames for specific WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output. Provides isConnectionProtocolEnabled(connection) utility to check if protocol messages are active for a given connection, persisting across Durable Object hibernation.
+5 more
show less
Releases @cloudflare/ai-chat v0.1.0 with support for typed JSON data parts (data-*) on messages alongside text content. Adds tool approval persistence in @cloudflare/ai-chat, surviving page refresh and DO hibernation by streaming to SQLite when a tool enters approval-requested state. Introduces maxPersistedMessages option in @cloudflare/ai-chat to cap SQLite message storage with automatic oldest-message deletion. Adds body option on the useAgentChat hook to send custom static or dynamic data with every request. Synchronizes getQueue() , getQueues() , getSchedule() , dequeue() , dequeueAll() , and dequeueAllByCallback() to return values directly instead of Promises, while remaining backward compatible with existing await calls.
10 details in Everything
Docker-in-Docker support added to Containers and Sandboxes
Feb 17, 2026
· release notes
Cloudflare Containers and Sandboxes now support Docker-in-Docker for running full sandboxed dev environments.
Assign Access policies to bookmark applications to control App Launcher visibility
Adds Access policy support to bookmark applications, allowing visibility control in the App Launcher based on identity and device posture. Bookmarks now respect standard Access policy configurations for filtering user access, excluding purpose justification, temporary authentication, and application isolation.
2 details in Everything
Quick Editor devtools replaced with log viewer
Feb 16, 2026
· release notes
Quick Editor devtools inspector replaced by log viewer
└──▷ USE IT
Migrate a Worker from the browser Quick Editor to local development using the new CLI command.
shell
copy
wrangler init --from-dash
Adds wrangler init --from-dash command to clone Quick Editor projects for local development.
1 detail in Everything
└──▷ BREAKING ON UPGRADE
! The Workers Quick Editor devtools inspector is deprecated and no longer available in the interface.
Content encoding support for Markdown for Agents and other improvements
Feb 16, 2026
· release notes
Adds text/markdown on-the-fly conversion for Cloudflare Agents with raised origin response limit and relaxed header requirements.
Raises the origin response limit from 1 MB to 2 MB (2,097,152 bytes) for Markdown conversion Removes the requirement for the origin to send the content-length header Adds support for content-encoded responses from the origin during Markdown conversion
3 details in Everything
Origin CA certificate support for Workers VPC
Feb 13, 2026
· release notes
Workers VPC VPC A logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware.
Fine-grained permissions for Access policies and service tokens
Feb 13, 2026
· release notes
Cloudflare adds Access policy admin and Access service token admin resource-scoped roles
Introduces the Cloudflare Access policy admin role to edit a specific Access policy in an account. Introduces the Cloudflare Access service token admin role to edit a specific Access service token in an account.
2 details in Everything
Cloudflare Python SDK v5.0.0-beta.1 now available
Prerelease
Feb 13, 2026
· release notes
Cloudflare Python SDK v5.0.0-beta.1 adds AI search, fraud detection, Radar data, R2 Data Catalog, and new CloudForce One endpoints.
Adds ai.tomarkdown resource for AI-powered markdown conversion Adds aisearch, aisearch.instances, and aisearch.tokens resources for AI-powered search functionality and instance management Adds fraud resource for fraud detection and prevention Adds radar.bots, radar.ct, and radar.geolocations resources for Radar bot analytics, certificate transparency data, and geolocation data Adds r2datacatalog, r2datacatalog.credentials, r2datacatalog.maintenanceconfigs, and r2datacatalog.namespaces resources for R2 Data Catalog integration
+4 more
show less
Adds cloudforceone.threatevents resource with new contentscanning() method Adds dns.records resource methods scan_list() , scan_review() , and scan_trigger() Adds radar.ai resource with summary() , timeseries() , and timeseries_groups() methods Adds organizations.organizationprofile resource for organization profile settings
9 details in Everything
└──▷ BREAKING ON UPGRADE
! The abusereports, acm.totaltls, apigateway.configurations, cloudforceone.threatevents, d1.database, intel.indicatorfeeds, logpush.edge, origintlsclientauth.hostnames, queues.consumers, radar.bgp, rulesets.rules, schemavalidation.schemas, snippets, and zerotrust.dlp resources have breaking changes! The zerotrust.networks resource has breaking changes
Introducing GLM-4.7-Flash on Workers AI, @cloudflare/tanstack-ai, and workers-ai-provider v3.1.1
Feb 13, 2026
· release notes
Workers AI adds GLM-4.7-Flash model, @cloudflare/tanstack-ai package for TanStack AI adapters, and transcription/speech/reranking reranking A model that re-scores a first batch of search results against the query and reorders them, more accurately than the fast first-stage search.
Adds GLM-4.7-Flash (model ID @cf/zai-org/glm-4.7-flash) with 131,072 token context window context window The maximum amount of text, counted in tokens, a model can take in and produce in one request. Everything the model knows about the task has to fit inside it. tool calling tool calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions. Introduces new @cloudflare/tanstack-ai npm package for TanStack AI adapters supporting Workers AI and AI Gateway Adds transcription (provider.transcription), text-to-speech (provider.speech), and reranking (provider.reranking) capabilities to workers-ai-provider v3.1.1
3 details in Everything
└──▷ BREAKING ON UPGRADE
! Deprecated createAutoRAG is replaced by createAISearch as the canonical export in workers-ai-provider v3.1.1 (though still functional with warning)
Cloudflare adds real-time HTML-to-Markdown conversion for AI agents via Accept header.
Adds text/markdown content negotiation support in the network edge to convert HTML to Markdown on the fly
1 detail in Everything
Enhanced Logo Matching for Brand Protection
Feb 12, 2026
· release notes
Cloudflare Brand Protection adds configurable logo match thresholds (75%-100%) and visual match scores in UI.
Users can now set a minimum match score starting at 75% when creating a logo query to capture subtle variations or high-quality impersonations Results table displays exact percentage of the match directly with color-coded lozenges to indicate severity Direct logo previews available in the Cloudflare dashboard similar to string matches to verify infringements at a glance
3 details in Everything
Anycast IPs displayed on the dashboard
Feb 12, 2026
· release notes
Cloudflare WAN dashboard now displays Anycast IPs for IPsec IPsec A suite of IETF protocols that authenticate and encrypt IP packets at the network layer, giving cyber tools a standards-based way to build VPNs or secure host-to-host tunnels without modifying applications. GRE GRE A tunneling protocol that wraps one network packet inside another, letting tools carry arbitrary traffic across IP networks without modifying the payload, useful for traffic capture and network emulation.
Anycast IP addresses are displayed directly in the Cloudflare WAN dashboard tunnel configuration form
1 detail in Everything
Adds AI Search and Workers Script data sources, placement controls, and Account tenant unit management in Terraform v5.17.0.
ai_search_instance data source now supports querying Cloudflare AI Search instancesai_search_token data source now supports querying Cloudflare AI Search tokensAccount resource unit field enables tenant unit management Account resource automatically maps managed_by.parent_org_id to unit.id workers_script adds placement.target array for targeted placement mode (region, hostname, host)
+3 more
show less
workers_script adds computed fields placement_mode and placement_statuszero_trust_dex_test data source adds filter support for specific testszero_trust_dlp_predefined_profile adds enabled_entries field for flexible entry management
8 details in Everything
Content Type Dimension for AI Bots in Cloudflare Radar
Feb 12, 2026
· release notes
Cloudflare Radar adds content_type dimension and API endpoints for AI bot traffic analysis.
Adds /ai/bots/summary/content_type endpoint to retrieve MIME type distribution for AI bots Adds /ai/bots/timeseries_groups/content_type endpoint for time-series AI bot content type data Enables filtering and grouping of Radar traffic by content_type dimension (HTML, JSON, Images, etc.)
3 details in Everything
Post-quantum encryption support for Cloudflare One Appliance
Feb 11, 2026
· release notes
Cloudflare One Appliance v2026.2.0 adds post-quantum post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA. ML-KEM ML-KEM NIST's post-quantum key-exchange standard (FIPS 203), formerly Kyber. Two parties use it to agree on a shared secret, usually alongside X25519 in a hybrid TLS handshake.
Adds post-quantum encryption support for Cloudflare One Appliance connections to the Cloudflare edge. Enables hybrid ML-KEM (Module-Lattice-Based Key-Encapsulation Mechanism) in TLS 1.3 handshakes between appliance and edge.
2 details in Everything
Workers are no longer limited to 1000 subrequests
Feb 11, 2026
· release notes
Workers subrequests limit increased from 1,000 to 10,000 (paid) with configurable cap up to 10M
Paid plan Workers now default to 10,000 subrequests per invocation instead of 1,000 Adds limits.subrequests config key in Wrangler to set custom subrequest caps up to 10,000,000 Allows setting limits.cpu_ms in Wrangler alongside subrequests to protect against runaway code
3 details in Everything
Improved React Server Components support in the Cloudflare Vite plugin
Feb 11, 2026
· release notes
Adds childEnvironments to Cloudflare Vite plugin for multi-environment Workers with improved React Server Components support
Adds childEnvironments config key to the Cloudflare Vite plugin to enable using multiple environments within a single Worker
1 detail in Everything
Interactive browser terminals in Sandboxes
Feb 9, 2026
· release notes
Sandbox SDK adds sandbox.terminal() and @cloudflare/sandbox/xterm for interactive browser-based terminals with PTY support.
Adds the sandbox.terminal(request) method to proxy a WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output. cols and rows configuration for terminal dimensions.
1 detail in Everything
AI Search now with more granular controls over indexing
Feb 9, 2026
· release notes
Cloudflare AI Search adds per-file reindexing and specific sitemap targeting via new UI paths
Adds Overview > Indexed Items sync icon for reindexing individual files without a full rescan Adds Settings > Parsing options > Specific sitemaps config path to limit crawler to a single sitemap URL
2 details in Everything
R2 SQL now supports approximate aggregation functions
Feb 9, 2026
· release notes
R2 SQL adds five new approximate aggregation functions for high-cardinality data analysis.
Adds APPROX_PERCENTILE_CONT(column, percentile) to return approximate percentile values with optional WHERE filters Adds APPROX_PERCENTILE_CONT_WITH_WEIGHT(column, weight, percentile) for weighted percentile calculations Adds APPROX_MEDIAN(column) to return the approximate median value Adds APPROX_DISTINCT(column) to count approximate distinct values across any column type Adds APPROX_TOP_K(column, k) to retrieve the k most frequent values as a JSON array
5 details in Everything
Log Explorer adds concurrent query tabs and filter pivot capabilities
Adds Tabs feature to Log Explorer for multiple concurrent queries Adds quick filtering from query results to current query Adds Cmd + click on filter button to pivot to new tab with applied filter
3 details in Everything
Cloudflare adds AI crawl control views: URI pattern grouping, referral trends, bytes toggles, and image exports for reports.
Adds a Patterns tab in Metrics > Most popular paths to group requests by URI patterns like /blog/* Adds a Referrals over time chart in Metrics to show AI-driven referral traffic trends by operator or source Adds a toggleable Bytes metric in Allowed requests over time chart and a new Bytes Transferred column in Crawlers tab Enables exporting charts and tables as images for reports and presentations
4 details in Everything
Agents SDK v0.4.0: Readonly connections, MCP security improvements, x402 v2 migration, and custom MCP OAuth providers
Feb 9, 2026
· release notes
Agents SDK v0.4.0 adds readonly connection hooks, custom MCP OAuth MCP OAuth An authentication layer for the Model Context Protocol that lets MCP clients obtain delegated access tokens so cyber tools can call MCP servers on a user's behalf without handling raw credentials. x402 x402 A proposed HTTP payment protocol revival using status code 402, enabling machine-to-machine micropayments over HTTP so cyber tools can gate API access or resources behind automated, per-request cryptocurrency payments.
Adds shouldConnectionBeReadonly, setConnectionReadonly, and isConnectionReadonly hooks to restrict WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output. Adds createMcpOAuthProvider method on the Agent class to enable custom OAuth providers for MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Adds callbackPath option to addMcpServer to prevent instance name leakage in MCP OAuth callback URLs
3 details in Everything
└──▷ BREAKING ON UPGRADE
! Deprecates onStateUpdate in favor of onStateChanged (drop-in rename)! Migration from x402 package to @x402/core and @x402/evm v2 packages! Updates PaymentRequirements type fields (e.g., maxAmountRequired to amount)! Changes X402ClientConfig.account type from viem.Account to ClientEvmSigner
Visualize data, share links, and create exports with the new Workers Observability dashboard
Feb 6, 2026
· release notes
New Workers Observability dashboard enables visualizations, data export, sharing, and UI customizations
Adds the ability to build charts directly in a Worker's Observability tab. Enables exporting logs and traces as JSON or CSV for offline analysis. Allows generating direct URLs to specific events, invocations, and traces that open standalone pages. Adds an improved field picker to add, remove, and reorder columns in the events table. Enables expanding events inline within the table to view full details without leaving the list.
+1 more
show less
Adds keyboard shortcut support for navigating the dashboard.
6 details in Everything
Visualize your Workflows in the Cloudflare dashboard
Feb 4, 2026
· release notes
Cloudflare adds beta workflow diagram visualization to the dashboard for JS/TS workflows
Enables UI toggles to collapse or expand loops and nested logic within generated workflow diagrams
1 detail in Everything
New Cloudflare Workers reference docs for AI Crawl Control with GraphQL API, Bot reference, and x402 x402 A proposed HTTP payment protocol revival using status code 402, enabling machine-to-machine micropayments over HTTP so cyber tools can gate API access or resources behind automated, per-request cryptocurrency payments.
Adds GraphQL API reference for querying crawler requests, top paths, referral traffic, and data transfer with filters for detection IDs, user agents, and referrer domains Adds Bot reference listing detection IDs and user agents for major AI crawlers from OpenAI, Anthropic, Google, Meta, and others
2 details in Everything
Agents SDK v0.3.7: Workflows integration, synchronous state, and scheduleEvery()
Feb 3, 2026
· release notes
Cloudflare Agents SDK v0.3.7 adds Workflows integration via AgentWorkflow class, synchronous state hooks, and scheduleEvery()
Adds AgentWorkflow class for first-class Cloudflare Workflows integration with durable execution steps Introduces validateStateChange() hook for synchronous state management in agents Adds scheduleEvery() method for fixed-interval recurring tasks with overlap prevention Adds runWorkflow() , getWorkflow() , getWorkflows() , approveWorkflow() , rejectWorkflow() , pauseWorkflow() , resumeWorkflow() , and terminateWorkflow() methods to the Agent class Exposes getCallableMethods() introspection API to discover callable methods
+3 more
show less
Adds streamingResponse.error() method for graceful stream error signaling Enables HMAC-SHA256 HMAC-SHA256 A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it. Adds basePath option to bypass default URL construction in agent client configuration
8 details in Everything
Threat actor identification with "also known as" aliases
Feb 3, 2026
· release notes
Cloudflare Threat Events now include an Also known as field with actor aliases in the dashboard and API.
Adds Also known as field to Cloudflare Threat Events providing common aliases for tracked groups Enables viewing the Also known as field by expanding the event details side panel under the Attacker field in the dashboard Allows adding the Also known as field as a column in the configurable table view within the Cloudflare dashboard
3 details in Everything
Improve Global Upload Performance with R2 Local Uploads - Now in Open Beta
Feb 3, 2026
· release notes
Cloudflare R2 adds local-uploads bucket feature in open beta to improve upload performance via the Wrangler CLI and Dashboard.
wrangler r2 bucket local-uploads enable <BUCKET_NAME> command enables Local Uploads on a bucket.Local Uploads option added to Cloudflare Dashboard bucket settings.
2 details in Everything
Improved Accessibility and Search for Monitoring
Feb 2, 2026
· release notes
New widget search and dedicated action buttons added to the Cloudflare Monitoring UI
Adds Widget Search functionality to the Policies, Submitters, and Impersonation widgets in the Monitoring page
1 detail in Everything
Magic WAN and Transit customers can now configure BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes. IPsec IPsec A suite of IETF protocols that authenticate and encrypt IP packets at the network layer, giving cyber tools a standards-based way to build VPNs or secure host-to-host tunnels without modifying applications. GRE GRE A tunneling protocol that wraps one network packet inside another, letting tools carry arbitrary traffic across IP networks without modifying the payload, useful for traffic capture and network emulation.
Enables establishing eBGP sessions between customer devices and Magic WAN/Magic Transit services when connected via IPsec or GRE tunnel on-ramps Adds MD5 authentication support for BGP sessions to prevent route hijacking or misconfiguration
2 details in Everything
Reduced minimum cache TTL for Workers KV to 30 seconds
Jan 30, 2026
· release notes
Workers KV now supports a minimum cacheTtl of 30 seconds via get() and getWithMetadata()
Adds support for cacheTtl: 30 in the get() method to reduce the minimum caching duration from 60 to 30 seconds. Adds support for cacheTtl: 30 in the getWithMetadata() method to reduce the minimum caching duration from 60 to 30 seconds.
2 details in Everything
Launching FLUX.2 [klein] 9B on Workers AI
Jan 28, 2026
· release notes
Cloudflare Workers AI launches FLUX.2 [klein] 9B image generation model with multi-reference support
Adds the @cf/black-forest-labs/flux-2-klein-9b model to Workers AI for image generation
1 detail in Everything
Cloudflare dashboard now supports UTC or browser/system timezone preference via user profile settings.
Adds Timezone preferences setting accessible from the user profile dropdown to display dates/times in UTC or local timezone.
1 detail in Everything
WARP client for Windows (version 2026.1.89.1)
Jan 27, 2026
· release notes
Windows WARP client adds NetBIOS over TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. MDM MDM Mobile device management, centrally configuring and managing enrolled devices. Administrators use it to apply settings, distribute applications and enforce device security policies.
Improves Multi-user mode so that switching from pre-login to user registration no longer loses MDM configuration association
1 detail in Everything
└──▷ BREAKING ON UPGRADE
! NetBIOS over TCP/IP is now disabled by default in the Windows WARP client; it must be explicitly enabled in device profile settings.
Configure Cloudflare source IPs (beta)
Jan 27, 2026
· release notes
Beta Unified Routing allows configuring Cloudflare source IPs for private network traffic.
Adds configurable IPv4 source IP range (100.64.0.0/12 by default) for traffic to private networks in Unified Routing (beta) Introduces new requirement: Cloudflare One Networks Write permission to configure source IPs Extends supported connectors to GRE GRE A tunneling protocol that wraps one network packet inside another, letting tools carry arbitrary traffic across IP networks without modifying the payload, useful for traffic capture and network emulation. IPsec IPsec A suite of IETF protocols that authenticate and encrypt IP packets at the network layer, giving cyber tools a standards-based way to build VPNs or secure host-to-host tunnels without modifying applications.
3 details in Everything
Increased Pages file limit to 100,000 for paid plans
Jan 23, 2026
· release notes
Cloudflare Pages raises file limit to 100k for paid plans via PAGES_WRANGLER_MAJOR_VERSION=4
Adds support for up to 100,000 files per Pages site on paid plans (up from 20,000)
1 detail in Everything
Vectorize indexes now support up to 10 million vectors
Jan 23, 2026
· release notes
Vectorize index capacity limit doubled to 10 million vectors
New account-level require access setting enforces deny-by-default for all zone hostnames.
Adds account-wide default-deny for Cloudflare Access to prevent accidental exposure of unconfigured hostnames
1 detail in Everything
New Wrangler config keys placement.region, host, and hostname for explicit Worker placement hints
Adds placement.region config key to .wrangler/config.json or wrangler.toml for AWS/GCP/Azure region hints Adds placement.host config key for layer 4 placement probes Adds placement.hostname config key for layer 7 placement probes Adds placement.mode config key to enable smart placement
4 details in Everything
New granular API token permissions for Cloudflare Access
Jan 22, 2026
· release notes
New granular API token permissions added for Cloudflare Access
Adds Access: Organizations Revoke permission for revoking user sessions in a Zero Trust organization Adds Access: Population Read permission for read-only access to SCIM SCIM A standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave. identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. Adds Access: Population Write permission for creating or modifying SCIM users and groups synced from an identity provider
3 details in Everything
New cryptographic functions — encode_base64() and sha256()
Jan 22, 2026
· release notes
Cloudflare Rulesets adds encode_base64() and sha256() functions for in-rule cryptography
Adds encode_base64(input, flags) function to enable Base64 encoding directly within Cloudflare Ruleset expressions. Adds sha256(input) function to compute SHA-256 SHA-256 A cryptographic hash function that turns data into a fixed 256-bit fingerprint. It is used to check integrity; hashing does not encrypt the original data.
2 details in Everything
Cloudflare Terraform Provider v5.16.0 adds BGP BGP A routing protocol that lets autonomous systems on the internet exchange reachability information, determining how traffic flows between networks. Cyber tools use it to monitor route hijacks or inject sinkholes.
Adds automatic_return_routing attribute to magic_wan_gre_tunnel resource for automatic routing control Adds automatic_return_routing attribute to magic_wan_ipsec_tunnel resource for automatic routing control Adds BGP configuration support with new bgp_model attribute to magic_wan_gre_tunnel resource Adds BGP configuration support with new bgp_model attribute to magic_wan_ipsec_tunnel resource Adds bgp_status computed attribute to magic_wan_gre_tunnel resource for BGP connection status information
+9 more
show less
Adds bgp_status computed attribute to magic_wan_ipsec_tunnel resource for BGP connection status information Adds custom_remote_identities attribute to magic_wan_ipsec_tunnel resource for custom identity configuration Enhances schema with BGP-related attributes and validators in magic_wan_gre_tunnel resource Enhances schema with BGP and identity-related attributes in magic_wan_ipsec_tunnel resource Adds request body buffering support to ruleset resource Enhances ruleset data source with additional configuration options Adds waf_challenge as new supported error page type identifier in custom_pages resource and data source schemas Adds observability logs attributes to list data source model in workers_script Enhances list data source schema with additional configuration options in workers_script
14 details in Everything
Import SQL files as additional modules by default
Jan 20, 2026
· release notes
Wrangler and Cloudflare Vite plugin now import .sql files as JavaScript strings by default
*.sql file extension is automatically configured to be importable in Worker code via Wrangler or the Cloudflare Vite plugin.SQL files are imported as JavaScript strings, eliminating the need for custom rules when using Drizzle.
2 details in Everything
Create AI Search instances programmatically via REST API
Jan 20, 2026
· release notes
New POST /accounts/{id}/ai-search/instances endpoint enables programmatic creation of AI Search instances.
Cloudflare Typescript SDK v6.0.0-beta.1 now available
Prerelease
Jan 20, 2026
· release notes
Cloudflare TS SDK v6 adds D1 Time Travel, MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. CRUD CRUD The four basic database operations — Create, Read, Update, Delete — used as shorthand for any system that manages persistent data records, giving cyber tools a standard model for interacting with stored information.
Adds client.d1.database.timeTravel methods getBookmark() and restore() for point-in-time recovery Adds client.aisearch client with full CRUD operations for Instances, Items, Jobs, and Tokens Adds createV1, listV1 and new sub-resources Sinks and Streams to the Pipelines client (client.pipelines) for v1 migration Adds mcp and mcp_portal as new ApplicationType values in Zero-Trust Access Applications Adds client.zeroTrust.access.aiControls.mcp client with CRUD methods for Portals and Servers
+1 more
show less
Adds detections.get() method to the Leaked Credential Checks client
6 details in Everything
└──▷ BREAKING ON UPGRADE
! DNS record interfaces renamed: e.g. RecordResponse.ARecord is now RecordResponse.A! Pipelines v0 API is deprecated; use createV1, listV1 methods instead! Origin CA csr, hostnames, and request_type params are now required in OriginCACertificateCreateParams! Radar V2 methods require the dimension parameter! Pipelines ConfigurationUpdateParams.properties is removed; use normalize! Removed CloudflaredCreateResponse, CloudflaredListResponse, CloudflaredDeleteResponse, CloudflaredEditResponse, CloudflaredGetResponse from Zero-Trust Tunnels
New functions for array and map operations
Jan 20, 2026
· release notes
Cloudflare Rulesets adds split, join, has_key, and has_value functions for advanced array and map expression logic
└──▷ TRY IT
Check if a specific country code exists in a custom response header list for access control.
copy
$ has_value(split(http.response.headers["x-allow-country"][0], ","), ip.src.country) Verify the presence of a custom header key in the request to filter traffic.
copy
$ has_key(http.request.headers, "x-custom-header") Combine an array of request header names into a comma-separated string for logging or comparison.
copy
$ join(http.request.headers.names, ", ")
split(source, delimiter) function added to Ruleset expressions to split strings into arrays.join(array, delimiter) function added to Ruleset expressions to combine arrays into a single string.has_key(map, key) function added to Ruleset expressions to check for the existence of a key in a map.has_value(map, value) function added to Ruleset expressions to check for the existence of a value in a map.
4 details in Everything
AI Search path filtering for website and R2 data sources
Jan 20, 2026
· release notes
AI Search adds path filtering for website and R2 data sources using micromatch patterns.
Enhanced HTTP/3 request cancellation visibility
Jan 19, 2026
· release notes
Cloudflare now terminates HTTP/3 HTTP/3 The third major version of HTTP, standardized by the IETF, which runs over QUIC instead of TCP, eliminating head-of-line blocking and reducing connection latency for faster, more resilient data transfer.
HTTP/3 clients cancelling requests are now terminated immediately at the edge rather than forwarded to the origin. Logs for terminated HTTP/3 request streams now report 499 status codes instead of upstream response codes.
2 details in Everything
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Cloudflare Managed Ruleset rule ...ad7dad3e (SQLi SQLi An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does. ...d32b798c.Cloudflare Managed Ruleset rule ...9e553ad3 (SQLi - Sub Query) now blocks instead of logs, merged into rule ...743e66b1.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! Managed ruleset detections previously logging SQL Injection attempts are now actively blocking traffic.
Verify WARP Connector connectivity with a simple ping
Jan 15, 2026
· release notes
WARP Connector now responds to pings on its LAN IP for immediate connectivity verification
WARP Connector responds to ICMP ping requests on its own LAN IP address
1 detail in Everything
Launching FLUX.2 [klein] 4B on Workers AI
Jan 15, 2026
· release notes
Workers AI now offers FLUX.2 [klein] 4B for fast image generation with multi-reference support.
Launches the @cf/black-forest-labs/flux-2-klein-4b model on Workers AI, a distilled variant optimized for speed and cost. Enables multi-reference image styling via the input_image_0 through input_image_3 multipart parameters in the REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Exposes a new fixed 4-step inference process for the FLUX.2 [klein] model via the Workers AI runtime.
3 details in Everything
Support for CrowdStrike device scores in User Risk Scoring
Jan 15, 2026
· release notes
Cloudflare One adds CrowdStrike device scores to User Risk Scoring for granular risk policies
Adds CrowdStrike low device score behavior to automatically escalate user risk Adds CrowdStrike medium device score behavior to automatically escalate user risk
2 details in Everything
Cloudflare dashboard reorganizes Network Services navigation under Routes, Connectors, and Insights.
Renames Magic Firewall policies to Firewall Policies in the dashboard navigation Moves Magic Transit and Magic WAN configuration items (IP Prefixes, GRE GRE A tunneling protocol that wraps one network packet inside another, letting tools carry arbitrary traffic across IP networks without modifying the payload, useful for traffic capture and network emulation. IPsec IPsec A suite of IETF protocols that authenticate and encrypt IP packets at the network layer, giving cyber tools a standards-based way to build VPNs or secure host-to-host tunnels without modifying applications. Routes and Connectors Relocates network analytics, health, and real-time analytics to the Insights section of the menu Renames Magic WAN Connectors and Connector On-Ramps to Appliances and Appliance profiles under Connectors > Appliances
4 details in Everything
URL Scanner now supports PDF report downloads
Jan 14, 2026
· release notes
URL Scanner adds PDF report export via dashboard UI for offline sharing of scan results.
Adds a PDF download option in the URL Scanner results page within the Cloudflare dashboard.
1 detail in Everything
WARP client for Windows (version 2025.10.186.0)
Jan 13, 2026
· release notes
WARP for Windows GA introduces external signal connectivity management and Antivirus posture check
Adds the ability to manage WARP client connectivity for all devices using an external signal from an on-premises HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate. Adds a new WARP client device posture check for Antivirus that verifies presence and update status Adds support for transparent HTTP proxying in addition to CONNECT-based proxying in Proxy mode
3 details in Everything
WARP client for macOS (version 2025.10.186.0)
Jan 13, 2026
· release notes
macOS WARP 2025.10.186 adds proxy mode support for transparent HTTP and global external signal management.
Proxy mode now supports transparent HTTP proxying in addition to the existing CONNECT-based proxying.Administrators can now manage WARP client connectivity for all devices in their fleet using an external signal sent from an on-premises HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate.
2 details in Everything
AI Crawl Control Read Only role now available
Jan 13, 2026
· release notes
New AI Crawl Control Read Only role for domain-level read-only access.
`wrangler types` now generates types for all environments
Jan 13, 2026
· release notes
wrangler types now generates types for all environments by default
└──▷ USE IT
Generate complete TypeScript types for all environments in your Wrangler configuration.
shell
copy
wrangler types
Generate TypeScript types for only the production environment bindings.
shell
copy
wrangler types --env production
wrangler types now collects bindings from all environments and includes them in the generated Env type by default.Added --env flag to wrangler types to generate types for only a specific environment.
2 details in Everything
WARP client for Linux (version 2025.10.186.0)
Jan 13, 2026
· release notes
Linux WARP client GA adds non-filesystem disk encryption posture check, transparent HTTP proxying support, and global device connectivity management via external signal.
Adds Linux disk encryption posture check support for dm-crypt and other non-filesystem encryption types Adds transparent HTTP proxying to the existing CONNECT-based Proxy mode Adds the ability to manage WARP client connectivity for all devices in a fleet using an external signal from an on-premises HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate.
3 details in Everything
Metro code field now available in Rules
Jan 12, 2026
· release notes
Cloudflare Ruleset Engine now supports ip.src.metro_code field for DMA-based location policies
└──▷ USE IT
Create a rule that matches traffic originating from the Washington DC metropolitan area to apply specific location-based policies.
text
copy
ip.src.metro_code eq "501"
Adds the ip.src.metro_code field to the Ruleset Engine, populated with Designated Market Area (DMA) data from the incoming request's IP address.
1 detail in Everything
Validate your generated types with `wrangler types --check`
Jan 12, 2026
· release notes
Wrangler adds wrangler types --check flag for validating generated types without writing to disk.
└──▷ TRY IT
Fail a CI pipeline if Wrangler config changes have not resulted in updated types.
copy
$ npx wrangler types --check
Shell tab completions for Wrangler CLI
Jan 9, 2026
· release notes
Wrangler adds wrangler complete CLI command to generate shell tab completions for Bash, Zsh, Fish, and PowerShell.
Get notified when your Workers builds succeed or fail
Jan 9, 2026
· release notes
Workers builds now publish events via Event Subscriptions for external notifications
Publishes Workers build start, success, failure, and cancellation events to a Queue for processing
1 detail in Everything
Cloudflare admin activity logs capture creation of DNS over HTTP (DoH) users
Jan 8, 2026
· release notes
Admin activity logs now capture creation of DNS over HTTP (DoH DoH DNS over HTTPS, an IETF standard (RFC 8484) that tunnels DNS queries inside encrypted HTTPS traffic, making resolution indistinguishable from web traffic and bypassing traditional DNS-based monitoring.
Workers Analytics Engine SQL now supports filtering using HAVING and LIKE
Jan 7, 2026
· release notes
Workers Analytics Engine SQL now supports HAVING clause and LIKE pattern matching operators
└──▷ TRY IT
Find log entries where blob1 starts with error using case-sensitive pattern matching.
copy
$ SELECT * FROM logs WHERE blob1 LIKE 'error%'
Adds HAVING clause to filter groups based on aggregate values after GROUP BY completes. Adds LIKE, NOT LIKE, ILIKE, and NOT ILIKE pattern matching operators with % and _ wildcards.
2 details in Everything
Build microfrontend applications on Workers
Jan 1, 2026
· release notes
Cloudflare Workers now supports building and deploying microfrontend applications via a new template with router logic.
Adds a microfrontends template to Cloudflare Workers that automatically creates a router Worker for splitting applications into independently deployable units. Enables framework flexibility by allowing multi-framework applications (e.g., Astro, Remix, Next.js) within a single microfrontend setup. Provides built-in request routing, HTML/CSS/header rewriting, asset path rewrites, preload capabilities, and View Transitions API support via the router Worker.
3 details in Everything
Breakout traffic visibility via NetFlow
Dec 31, 2025
· release notes
Magic WAN Connector now exports NetFlow data for breakout traffic to Magic Network Monitoring (MNM)
Agents SDK v0.3.0, workers-ai-provider v3.0.0, and ai-gateway-provider v3.0.0 with AI SDK v6 support
Dec 22, 2025
· release notes
Agents SDK v0.3.0 adds dynamic tool approval via needsApproval and server-side tool() definition for human-in-the-loop human-in-the-loop Human in the loop, involving a person in an otherwise automated workflow. The person can review, approve, correct or supply information before work continues.
Adds the needsApproval option to the server-side tool() function to conditionally require user confirmation for agent tools. Introduces the unified tool() function on the server, replacing the client-side AITool pattern for defining agent capabilities. Adds the onToolCall callback parameter to useAgentChat(options) to handle client-side tool execution and output. Adds support for sending files and images to Workers AI models via the file part type in messages, with automatic conversion by the provider.
4 details in Everything
└──▷ BREAKING ON UPGRADE
! The CoreMessage type has been removed; use ModelMessage instead.! The mode option for generateObject has been removed and must be omitted from the call signature.! The convertToModelMessages() function is now asynchronous; all calls must now await the result.
Static prerendering support for TanStack Start
Dec 19, 2025
· release notes
Static prerendering support for TanStack Start apps allows serving build-time rendered HTML as static assets.
Enables prerender.enabled in the tanstackStart() Vite plugin config to prerender routes to static HTML at build time Serves prerendered routes as static assets accessible via Cloudflare Workers Provides access to build-time environment variables and bindings during prerendering
3 details in Everything
Cloudflare Terraform provider v5.15 adds ai_search resource and new attributes for DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Adds ai_search resource to support AI Search endpoints Adds forensic_copy attribute to zero_trust_gateway_policy resource Supports category, location, and device types in zero_trust_list resource Adds startup_time_ms attribute to worker_version resource Adds upload_status attribute to zero_trust_dlp_custom_entry, zero_trust_dlp_entry, zero_trust_dlp_integration_entry, and zero_trust_dlp_predefined_entry resources
5 details in Everything
R2 Data Catalog now supports automatic snapshot expiration
Dec 18, 2025
· release notes
R2 Data Catalog now supports automatic snapshot expiration for Iceberg tables via wrangler CLI.
Adds the new subcommand npx wrangler r2 bucket catalog snapshot-expiration enable to configure automatic retention policies for Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS. Introduces --older-than-days <N> and --retain-last <N> CLI arguments to define which snapshots are eligible for removal.
2 details in Everything
Cloudflare adds new default AI Crawl Control Overview tab with executive summary and operator grouping
Makes the Overview tab the default view in AI Crawl Control, replacing the previous crawl-specific controls as the landing page Adds an Executive summary dashboard to monitor total requests, volume change, most common status code, most popular path, and high-volume activity Adds Operator grouping to track crawlers by operating companies (OpenAI, Microsoft, Google, ByteDance, Anthropic, Meta) Adds Customizable filters to snapshot AI traffic by date range, crawler, operator, hostname, or path
4 details in Everything
Retrieve your authentication token with `wrangler auth token`
Dec 18, 2025
· release notes
Wrangler adds wrangler auth token command to retrieve current authentication credentials for scripts and other tools.
└──▷ USE IT
Get the current auth token in a script for use with other tools.
shell
copy
wrangler auth token
Retrieve structured JSON output to determine token type and values programmatically.
shell
copy
wrangler auth token --json
Adds the wrangler auth token command which retrieves the currently configured authentication token or credentials, prioritizing API token from CLOUDFLARE_API_TOKEN then OAuth token from wrangler login. Adds --json flag to wrangler auth token for structured output structured output Forcing a model's response to match a given format or JSON schema, so software can parse it reliably instead of hoping the text is well formed.
2 details in Everything
Workers for Platforms - Dashboard Improvements
Dec 18, 2025
· release notes
Workers for Platforms dashboard now supports namespace creation, dispatch worker templates, tag management, binding visibility, and one-click vibe coding platform deployment.
Adds Namespace Management to create and configure dispatch namespaces directly within the dashboard Adds Dispatch Worker Templates to define traffic routing to individual Workers within a namespace Adds Tag Management to set and update tags on User Workers via the UI Shows Bindings attached to User Workers directly within the User Worker view in the dashboard Adds one-click deployment of a reference implementation for an AI vibe coding platform powered by VibeSDK
5 details in Everything
Shadow IT - domain level SaaS analytics
Dec 17, 2025
· release notes
Zero Trust Shadow IT analytics now supports domain-level data transfer metrics and filtering.
Adds domain-level data transfer visibility to the Zero Trust Shadow IT dashboard Enables filtering of Shadow IT metrics by user, application, or content category
2 details in Everything
New duplicate action for supported Cloudflare One resources
Dec 16, 2025
· release notes
Cloudflare One dashboard adds a Duplicate action for Access Applications, Policies, and Gateway Policies.
Adds a Duplicate action in the Cloudflare One dashboard overflow menu (⋮) to clone Access Applications. Adds a Duplicate action in the Cloudflare One dashboard overflow menu (⋮) to clone Access Policies. Adds a Duplicate action in the Cloudflare One dashboard overflow menu (⋮) to clone Gateway Policies.
3 details in Everything
Configure your framework for Cloudflare automatically
Dec 16, 2025
· release notes
Wrangler 4.55 adds --x-autoconfig flag and wrangler setup command for automatic framework configuration
└──▷ USE IT
Deploy a framework or static site to Cloudflare Workers with automatic configuration instead of manual adapter installation.
shell
copy
npx wrangler deploy --x-autoconfig
Adds the --x-autoconfig flag to npx wrangler deploy to automatically configure and deploy supported frameworks (Next.js, Astro, Nuxt, TanStack Start, SolidStart, React Router, SvelteKit, Docusaurus, Qwik, Analog) and static sites without manual setup.
1 detail in Everything
Support for ctx.exports in @cloudflare/vitest-pool-workers
Dec 16, 2025
· release notes
@cloudflare/vitest-pool-workers now supports ctx.exports API for accessing top-level Worker exports in tests.
Adds support for the ctx.exports API via createExecutionContext() in @cloudflare/vitest-pool-workers to access a Worker's top-level exports during unit testing Enables importing exports directly from the cloudflare:workers module within tests
2 details in Everything
R2 SQL now supports aggregations and schema discovery
Dec 12, 2025
· release notes
R2 SQL adds aggregation functions (COUNT, SUM, etc.) and schema discovery commands to wrangler.
Adds GROUP BY support for aggregating data across dimensions in R2 SQL queries. Adds HAVING clause support to filter aggregated results in R2 SQL. Adds new SQL aggregation functions (COUNT, SUM, AVG, MIN, MAX) for Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS. Adds the SHOW DATABASES and SHOW NAMESPACES metadata commands to list available namespaces. Adds the SHOW TABLES IN namespace_name command to list tables within a specific namespace.
+1 more
show less
Adds the DESCRIBE namespace_name.table_name command to view table schema and column types.
6 details in Everything
Cloudflare Logpush adds native SentinelOne destination support via UI or API.
Pay Per Crawl (Private beta) - Discovery API, custom pricing, and advanced configuration
Dec 10, 2025
· release notes
Pay Per Crawl adds Discovery API for domain discovery, crawler-error header, free page rules, and payment header signing
Adds the GET https://crawlers-api.ai-audit.cfdata.org/charged_zones endpoint to programmatically discover domains participating in Pay Per Crawl. Allows site owners to configure free pages via Rules > Configuration Rules by setting URI patterns on URI Full and enabling the Disable Pay Per Crawl setting.
2 details in Everything
WAF Release - 2025-12-10 - Emergency
Dec 10, 2025
· release notes
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Adds Generic - Server Function Source Code Exposure detection (Rule ID ...74746aff) to the Cloudflare Free Ruleset with a Block action Adds Generic - Server Function Resource Exhaustion detection (Rule ID ...102ec699) to the Cloudflare Managed Ruleset in Disabled state
2 details in Everything
WARP client for macOS (version 2025.10.118.1)
Dec 9, 2025
· release notes
macOS WARP beta adds transparent HTTP proxying support alongside Local Domain Fallback fixes.
Proxy mode now supports transparent HTTP proxying in addition to existing CONNECT-based proxying.
1 detail in Everything
WARP client for Windows (version 2025.10.118.1)
Dec 9, 2025
· release notes
WARP Windows Beta adds transparent HTTP proxying alongside existing CONNECT mode
Proxy mode now supports transparent HTTP proxying in addition to CONNECT-based proxying.
1 detail in Everything
Easy Python package management with Pywrangler
Dec 8, 2025
· release notes
Introduces Pywrangler tooling for automatic Python dependency bundling in Cloudflare Workers via pyproject.toml and new CLI commands.
└──▷ TRY IT
Run the local development server for your Python Worker using Pywrangler.
copy
$ uv run pywrangler dev Deploy the Python Worker with all dependencies automatically bundled by Pywrangler.
copy
$ uv run pywrangler deploy
Adds Pywrangler, a new tool that automatically downloads and vendors Workers-compatible Python packages for bundling with your Worker Supports specifying Python dependencies in pyproject.toml using standard [project] dependencies and [dependency-groups] dev sections Provides uv run pywrangler dev command to develop a Worker locally Provides uv run pywrangler deploy command to deploy the bundled Worker
4 details in Everything
Wrangler config is optional when using Vite plugin
Dec 8, 2025
· release notes
Wrangler config now optional for assets-only sites via Vite plugin, generating defaults automatically
wrangler.toml, wrangler.json, and wrangler.jsonc are now optional when using the Cloudflare Vite plugin for assets-only (static) sites; if none are found the plugin generates sensible defaultsDefault name is derived from package.json or the project directory name Default compatibility_date uses the latest date supported by your installed Miniflare version
3 details in Everything
Configure Workers programmatically using the Vite plugin
Dec 8, 2025
· release notes
Cloudflare Vite plugin adds config option for programmatic Worker settings
One-click Access protection for Workers now creates reusable Cloudflare Access policies
Dec 4, 2025
· release notes
One-click Worker Access protection now creates reusable Cloudflare Access policies instead of per-app ones.
Workers preview URLs now share a single Cloudflare Workers Preview URLs policy across the account. Production workers.dev URLs now get their own reusable policy named <worker-name> - Production by default.
2 details in Everything
Connect to remote databases during local development with wrangler dev
Dec 4, 2025
· release notes
wrangler dev now supports direct remote database connections via localConnectionString config and env vars
wrangler dev now connects directly to remote databases and those requiring TLS without the --remote flag.Adds localConnectionString field to Hyperdrive bindings in wrangler configuration to specify remote connection details for local development. Introduces CLOUDFLARE_HYPERDRIVE_LOCAL_CONNECTION_STRING_<BINDING_NAME> environment variable as an alternative way to configure the local connection string.
3 details in Everything
Emergency WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives. deserialization deserialization Turning stored or transmitted data back into objects a program can use. Unsafe handling of untrusted data can allow unexpected behavior or code execution.
Deploys Cloudflare Managed Ruleset rule ID ...5fb92fba to block the RCE Generic - Framework vulnerability. Deploys Cloudflare Free Ruleset rule ID ...99702280 to block the same RCE vulnerability for free-tier accounts.
2 details in Everything
Agents SDK v0.2.24 with resumable streaming, MCP improvements, and schedule fixes
Nov 26, 2025
· release notes
Agents SDK v0.2.24 adds resumable streaming to AIChatAgent and redesigned MCPClientManager API.
AIChatAgent supports resumable streaming for reconnecting clientsMCPClientManager.registerServer() allows registering MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. MCPClientManager.connectToServer(id) establishes connection to a registered serverMCPConnectionState enum added with idle, connecting, authenticating, connected, discovering, and ready statesMCPClientConnection.discover() method with AbortController support and configurable timeout
5 details in Everything
New Zombie API detection for API Shield
Nov 25, 2025
· release notes
API Shield now automatically detects and labels zombie endpoints after 32 days of inactivity.
Adds cf-risk-zombie risk label to API Shield for endpoints with no traffic for 32+ days
1 detail in Everything
Launching FLUX.2 [dev] on Workers AI
Nov 25, 2025
· release notes
Workers AI launches FLUX.2 [dev] with multi-reference image inputs and JSON prompting capabilities
Adds @cf/black-forest-labs/flux-2-dev model to Workers AI for high-fidelity image generation with physical world grounding Supports up to four input_image_0, input_image_1, input_image_2, and input_image_3 parameters for multi-reference style transfer via multipart form data Enables granular control over generated images by passing a structured JSON object as the value for the prompt field in the API request
3 details in Everything
Cloud Services Observability in Cloudflare Radar
Nov 24, 2025
· release notes
Cloudflare Radar introduces HTTP Origins API endpoints and UI visibility for cloud origin infrastructure monitoring.
Adds GET /origins endpoint to list all origins (cloud providers and associated regions) Adds GET /origins/{origin} endpoint to retrieve information about a specific origin Adds GET /origins/timeseries endpoint to retrieve normalized time series data including REQUESTS, CONNECTION_FAILURES, RESPONSE_HEADER_RECEIVE_DURATION, TCP_HANDSHAKE_DURATION, and TCP_RTT metrics Adds GET /origins/summary endpoint to retrieve HTTP requests summarized by dimension (region, success_rate, percentile) Adds GET /origins/timeseries_groups endpoint to retrieve timeseries data grouped by dimension
+2 more
show less
Extends Annotations API to support origin outages for automated detection and alerting Extends Traffic Anomalies API to support origin anomalies for automated detection and alerting
7 details in Everything
Environment variable limits increase for Workers Builds
Nov 21, 2025
· release notes
Workers Builds env var limit raised to 64 vars with 5 KB each
Cloudflare Containers now support mounting R2 buckets as FUSE FUSE A Linux kernel interface that lets userspace programs implement a filesystem without kernel code, maintained as part of the kernel project; tools use it to mount virtual or synthetic filesystems without requiring root or kernel modules.
Containers can now mount R2 buckets as FUSE (Filesystem in Userspace) volumes, allowing applications to interact with R2 using standard filesystem operations.
1 detail in Everything
Cloudflare Terraform v5.13 adds cloudflare_connectivity_directory resource and new ZT features
Adds cloudflare_sso_connector as a new Terraform resource for SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. Adds cloudflare_universal_ssl_setting as a new Terraform resource for universal SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination. Adds proxy_endpoint attribute to the zero_trust_access_application resource for ZT Access Applications Adds support for self-serve license keys in the magic_transit_connector resource
4 details in Everything
└──▷ BREAKING ON UPGRADE
! The cloudflare_api_token and cloudflare_account_token resources have breaking changes to eliminate configuration drift caused by policy ordering differences; see the detailed Repository changelog for migration steps
AI Search support for crawling login protected website content
Nov 19, 2025
· release notes
Adds Extra headers configuration in AI Search to crawl login-protected sites via custom HTTP headers.
Enables custom HTTP header injection for AI Search website crawling to access authentication-protected content Adds a limit of five custom headers per Website data source in AI Search instance configuration
2 details in Everything
Adjustment to Final Disposition Column
Nov 18, 2025
· release notes
UI label and value updates for email security submission tracking.
New Cloudflare One Navigation and Product Experience
Nov 17, 2025
· release notes
Cloudflare One Zero Trust dashboard restructured with new navigation, search, and guided tour.
└──▷ HOW TO FIND IT
Revisit the onboarding tour to understand the new navigation structure.
📍 Overview › Get Started
Adds Zero Trust dashboard search to find product pages by both their new and old names Adds a guided login experience that can be replayed in Overview > Get Started
2 details in Everything
Generate Cloudflare Access SSH certificate authority (CA) directly from the Cloudflare dashboard
Nov 14, 2025
· release notes
Add 'Generate Cloudflare Access SSH certificate authority (CA) directly from the Cloudflare dashboard', enabling UI-based CA management
New SaaS Security weekly digests with API CASB
Nov 14, 2025
· release notes
New opt-in CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic. SaaS SaaS Software delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally.
Adds the CASB Weekly Digest notification type to deliver a Monday morning email summary of API CASB findings, high/critical risks, and integration health status.
1 detail in Everything
Log Explorer adds 14 new datasets including DNS firewall logs and BISO user actions for deeper visibility.
Adds support for DNS firewall logs , BISO_user_actions, and Audit_logs_v2 in Log Explorer. Adds support for Dns_logs, Nel_reports, Page_shield_events, Spectrum_events, and Zaraz_events datasets. Adds support for Account Level Audit Logs, Email_security_alerts, Magic Firewall IDS , Network Analytics , Sinkhole HTTP , and ipsec_logs.
3 details in Everything
DEX Logpush jobs now export WARP/DEX device data sets to R2, cloud buckets, or SIEM SIEM Security information and event management, collecting logs from many systems and correlating events to find suspicious activity. Analysts use it to investigate alerts and incidents.
Adds four new WARP and DEX device data sets (DEX Application Tests, DEX Device State Events, WARP Config Changes, WARP Toggle Changes) exportable via Cloudflare Logpush
1 detail in Everything
More SQL aggregate, date and time functions available in Workers Analytics Engine
Nov 12, 2025
· release notes
Workers Analytics Engine adds countIf, sumIf, avgIf aggregate functions and extensive date/time SQL functions
Adds countIf(condition) to count rows satisfying a condition Adds sumIf(condition) to calculate sums from rows satisfying a condition Adds avgIf(condition) to calculate averages from rows satisfying a condition Adds date/time functions: toYear() , toMonth() , toDayOfMonth() , toDayOfWeek() , toHour() , toMinute() , toSecond() Adds date/time functions: toStartOfYear() , toStartOfMonth() , toStartOfWeek() , toStartOfDay() , toStartOfHour()
+2 more
show less
Adds date/time functions: toStartOfFifteenMinutes() , toStartOfTenMinutes() , toStartOfFiveMinutes() , toStartOfMinute() Adds today() and toYYYYMM() date/time functions
7 details in Everything
New BOLA Vulnerability Detection for API Shield
Nov 12, 2025
· release notes
API Shield adds automatic BOLA BOLA Broken Object Level Authorization, an API vulnerability class where a server fails to verify that the requesting user owns or may access the object ID they supply, letting attackers read or modify other users' data.
WARP client for Linux (version 2025.9.558.0)
Nov 11, 2025
· release notes
WARP client for Linux GA release adds PMTUD support and improved tunnel health status
Path Maximum Transmission Unit Discovery (PMTUD) is now supported to dynamically adjust packet sizing, disabled by default GUI GUI A graphical user interface, controls such as windows, buttons and menus. It lets people use software visually rather than entering commands.
2 details in Everything
Resize your custom SQL window in Log Explorer
Nov 11, 2025
· release notes
Users can now resize the custom SQL query window in Log Explorer's UI for better visibility of complex queries
Enables resizing of the custom SQL query window in Log Explorer by dragging its bottom edge to view longer queries without scrolling
1 detail in Everything
Cloudflare introduces Logpush Health Dashboards for real-time job visibility
Adds Upload Health and Upload Reliability sections to the new Health tab in the Cloudflare dashboard, providing data completeness, success rate, retry counts, and latency metrics for Logpush jobs. Enables access to these health dashboards at the account or zone level via the existing Cloudflare dashboard interface.
2 details in Everything
WARP client for Windows (version 2025.9.558.0)
Nov 11, 2025
· release notes
Windows WARP client GA release adds PMTUD support, Windows 11 ARM ARM A family of RISC processor architectures designed by Arm Holdings and licensed to chip makers worldwide; tools target it to run natively on mobile, embedded, and increasingly server and desktop hardware.
Adds PMTUD (Path Maximum Transmission Unit Discovery) to dynamically adjust packet sizing for connection optimization Adds steps in the GUI GUI A graphical user interface, controls such as windows, buttons and menus. It lets people use software visually rather than entering commands. Adds support for Windows 11 ARM-based machines
3 details in Everything
Crawler drilldowns with extended actions menu
Nov 10, 2025
· release notes
Adds per-crawler drilldowns with extended actions menu and status code analytics in AI Crawl Control
└──▷ HOW TO FIND IT
Access status code distribution for all crawlers to identify traffic patterns.
📍 Go to AI Crawl Control › Metrics
Status code distribution chart on the Metrics tab to analyze HTTP response codes (2xx, 3xx, 4xx, 5xx) over time Per-crawler extended actions menu with View Metrics , View on Cloudflare Radar , Copy User Agent , View in Security Analytics , and Copy Detection ID options
2 details in Everything
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Adds detection rules for Prototype Pollution via URI (...606285e6) Adds detection rules for Prototype Pollution via Body (...4f59ff26) Adds detection rules for Prototype Pollution via Header - Form (...7efbeb39)
3 details in Everything
Select Wrangler environments using the CLOUDFLARE_ENV environment variable
Nov 9, 2025
· release notes
Wrangler now reads CLOUDFLARE_ENV env var to select Worker environments, streamlining CI/CD workflows.
Adds support for the CLOUDFLARE_ENV environment variable to select the active environment for Wrangler commands that support the --env flag.
1 detail in Everything
Inspect Cache Keys with Cloudflare Trace
Nov 7, 2025
· release notes
Cloudflare Trace now exposes the exact generated cache key in the cache object for debugging.
Enables direct inspection of cache keys in Cloudflare Trace UI
1 detail in Everything
Workers automatic tracing, now in open beta
Nov 7, 2025
· release notes
Cloudflare Workers open beta for automatic tracing with configurable observability and OTLP OTLP OpenTelemetry Protocol, a standard way to send traces, metrics and logs between applications, collectors and monitoring systems. It lets telemetry move across compatible tools.
Enables observability.traces.enabled config to activate automatic tracing on Cloudflare Workers Exports traces and correlated logs to OTLP-compatible destinations via the Cloudflare dashboard Displays traces alongside logs in the Workers Observability dashboard Allows querying span attributes including operation type, status, duration, and errors
4 details in Everything
Magic WAN adds Automatic Return Routing beta for route-less symmetric return traffic
Adds Automatic Return Routing (ARR) support in Magic WAN, enabling customers to configure Magic on-ramps (IPsec IPsec A suite of IETF protocols that authenticate and encrypt IP packets at the network layer, giving cyber tools a standards-based way to build VPNs or secure host-to-host tunnels without modifying applications. GRE GRE A tunneling protocol that wraps one network packet inside another, letting tools carry arbitrary traffic across IP networks without modifying the payload, useful for traffic capture and network emulation. Introduces Route-less mode where static or dynamic routes are optional when using ARR. Enables Overlapping IP space support allowing traffic from customer sites to use overlapping private IP ranges. Guarantees Symmetric routing by ensuring return traffic uses the same connection as the original on-ramp. Requisite feature requires enabling the new Unified Routing mode (beta).
5 details in Everything
Designate WAN link for breakout traffic
Nov 6, 2025
· release notes
Magic WAN Connector lets you designate a specific WAN port for application breakout traffic.
Applications to be remapped to the new categories
Nov 6, 2025
· release notes
Cloudflare Gateway remaps application categories for refined HTTP traffic policies.
Applications are remapped to new category values (e.g., File Sharing becomes Photography & Graphic Design), allowing policies to target more precise app types. A transition period is provided until January 30, 2026, for administrators to update existing Gateway rules to use the new categories before old mappings change.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! Existing Gateway policies targeting old application categories (e.g., File Sharing , Human Resources ) will stop matching traffic as of January 30, 2026.
Announcing Workers VPC Services (Beta)
Nov 5, 2025
· release notes
Introduces Workers VPC VPC A logically isolated virtual network inside a public cloud provider's infrastructure, letting tools deploy resources with private addressing, controlled routing, and firewall rules without managing physical hardware.
Announces Workers VPC Services (Beta), enabling Workers to securely access resources in private networks without exposing them on the public Internet Adds support for connecting to resources in any external cloud (AWS, Azure, GCP) or on-premise using Cloudflare Tunnels via Multi-cloud Support
2 details in Everything
D1 can restrict data localization with jurisdictions
Nov 5, 2025
· release notes
D1 databases now support jurisdiction-based data localization via the jurisdiction flag and API field.
Adds the --jurisdiction flag to wrangler d1 create for specifying eu or fedramp data residency at database creation Adds the jurisdiction field support in the POST /client/v4/accounts/{account_id}/d1/database API request body
2 details in Everything
Log Explorer now shows query result distribution
Nov 4, 2025
· release notes
Log Explorer adds a dynamic Query results distribution chart for temporal analysis
Log Explorer now supports query cancellation
Nov 4, 2025
· release notes
Log Explorer now supports canceling currently running queries to improve investigative workflow
Adds the ability to cancel a query that is currently running in Log Explorer
1 detail in Everything
Capture Wrangler command output in structured format
Nov 3, 2025
· release notes
Adds WRANGLER_OUTPUT_FILE_PATH and WRANGLER_OUTPUT_FILE_DIRECTORY env vars to capture Wrangler output in structured ND-JSON format for automation.
Enables programmatic access to deployment information by setting WRANGLER_OUTPUT_FILE_PATH or WRANGLER_OUTPUT_FILE_DIRECTORY environment variables. Captures Wrangler command output in structured ND-JSON format for supported commands including wrangler deploy, wrangler versions upload, wrangler versions deploy, and wrangler pages deploy.
2 details in Everything
Report logo misuse to Cloudflare directly from the Brand Protection dashboard
Oct 31, 2025
· release notes
Brand Protection dashboard adds Report to Cloudflare button for direct logo misuse abuse reports.
Workers WebSocket message size limit increased from 1 MiB to 32 MiB
Oct 31, 2025
· release notes
Cloudflare Workers WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output.
New TCP-based fields available in Rulesets
Oct 30, 2025
· release notes
New cf.edge.client_tcp and cf.timings.client_tcp_rtt_msec fields in Cloudflare Rulesets
Adds cf.edge.client_tcp boolean field to detect if a request used TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. QUIC QUIC A UDP-based transport protocol standardized by the IETF that bakes in TLS 1.3, multiplexed streams, and connection migration, giving tools low-latency encrypted transport without head-of-line blocking. Adds cf.timings.client_tcp_rtt_msec numeric field providing smoothed client-to-Cloudflare TCP round-trip time
2 details in Everything
Access Workers preview URLs from the Build details page
Oct 30, 2025
· release notes
Access Workers preview URLs directly from the Build details page via a new Preview button.
Adds a Preview button in the top-right corner of the build details page for successful builds to open the latest preview URL
1 detail in Everything
Introducing email two-factor authentication
Oct 30, 2025
· release notes
Cloudflare adds email as a supported two-factor authentication factor for all accounts.
Adds email as a new authentication factor in the Two-Factor Authentication settings. Enables users to set up email-based 2FA via the Profile > Authentication > Two-Factor Authentication > Set up UI path.
2 details in Everything
Cloudflare revamps Member Management UI with multi-account policy assignment and enhanced permission visibility
Administrators can now assign multiple account-scoped policies to a single member
1 detail in Everything
New Application Categories added for HTTP Traffic Management
Oct 28, 2025
· release notes
Gateway introduces new granular HTTP application categories for policy creation.
Adds Business , Education , Entertainment & Events , Food & Drink , Health & Fitness , Lifestyle , Navigation , Photography & Graphic Design , and Travel application categories to Gateway HTTP policies
1 detail in Everything
Cloudflare CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic. IAM IAM Identity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access.
Reranking and API-based system prompt configuration in AI Search
Oct 28, 2025
· release notes
AI Search adds rerankingreranking A model that re-scores a first batch of search results against the query and reorders them, more accurately than the fast first-stage search. system_prompt support for dynamic control.
Adds the reranking field to AI Search API requests, allowing configuration of a reranker reranker A model that re-scores a first batch of search results against the query and reorders them, more accurately than the fast first-stage search. @cf/baai/bge-reranker-base) to reorder retrieved documents by semantic relevance Enables passing system_prompt directly in AI Search API requests for per-query dynamic control over assistant behavior
2 details in Everything
Access private hostname applications support all ports/protocols
Oct 28, 2025
· release notes
Cloudflare Access now supports securing private applications on all ports and protocols, removing the previous HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate. SNI SNI A TLS extension that lets a client declare which hostname it is connecting to during the handshake, allowing one server to host multiple certificates on a single IP address.
Removes the previous requirement that private hostname applications use HTTPS on port 443 with Server Name Indicator (SNI), enabling support for SSH, RDP RDP A Microsoft protocol that lets a user view and control a remote Windows desktop over a network, giving cyber tools a standard channel to audit, attack-simulate, or monitor Windows systems remotely.
1 detail in Everything
Cloudforce One RFI tokens are now visible in the dashboard
Oct 27, 2025
· release notes
Cloudforce One RFI tokens and remaining balance are now visible in the Threat Intelligence dashboard.
Adds visibility of tokens used for each submitted Request for Information (RFI) in the Cloudforce One dashboard Adds display of remaining quarterly token balance for the account in the Cloudforce One dashboard
2 details in Everything
Cloudflare Radar adds TLD TLD The rightmost label in a domain name (e.g., .com, .gov, .uk), maintained by IANA's root zone. Cyber tools filter or pivot on TLDs to scope scans, flag suspicious registrations, or classify traffic by geography or type. /tlds API endpoints and DNS query dimensions
Adds /tlds endpoint to list all Top-Level Domains (TLDs) in Radar Adds /tlds/{tld} endpoint to retrieve detailed TLD information including type, manager, DNSSEC DNSSEC A set of DNS extensions, maintained by the IETF, that add cryptographic signatures to DNS records so resolvers can verify responses have not been tampered with in transit. RDAP RDAP A JSON-based protocol for querying domain and IP registration data, standardized by the IETF as a modern replacement for WHOIS, giving cyber tools structured, machine-readable ownership and contact lookups. Adds tld filter and tld_dns_magnitude dimension to existing /dns/summary/{dimension} and /dns/timeseries_groups/{dimension} endpoints
3 details in Everything
Logpush now supports a Codeless Connector Framework-based integration with Azure Sentinel for native log ingestion.
Adds support for the new Azure Sentinel Connector built on Microsoft's Codeless Connector Framework (CCF) Enables configuration of Data Collection Rules (DCRs) to filter and transform logs at ingestion time Provides native integration with Azure Data Lake for log storage
3 details in Everything
Automatic resource provisioning for KV, R2, and D1
Oct 24, 2025
· release notes
Wrangler 4.45.0 adds automatic provisioning for KV, R2, and D1 resources via wrangler deploy
Build TanStack Start apps with the Cloudflare Vite plugin
Oct 24, 2025
· release notes
Release introduces TanStack Start integration into the Cloudflare Vite plugin and CLI, enabling new project scaffolding and SSR configuration for Workers.
└──▷ USE IT
Scaffold a new TanStack Start app ready for Cloudflare Workers deployment via the CLI.
shell
copy
npm create cloudflare@latest -- my-tanstack-start-app --framework=tanstack-start
Adds --framework=tanstack-start argument to the create cloudflare CLI command.
1 detail in Everything
Workers Preview URL default behavior now matches your workers.dev setting
Oct 23, 2025
· release notes
Workers Preview URLs now default to matching workers.dev setting in Wrangler v4.44.0+
Preview URLs default to enabled when workers.dev is enabled, and disabled when workers.dev is disabled (Wrangler >= v4.44.0). Explicit configuration of preview URL settings remains supported via the Dashboard, API, or Wrangler to override the new default.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! Wrangler v4.44.0+ changes the default behavior of Preview URLs from always enabled (v4.34.0-<v4.44.0: disabled) to matching the workers.dev route state.! Existing Workers with workers.dev route disabled had a one-time update to disable preview URLs.
Workers AI Markdown Conversion: New endpoint to list supported formats
Oct 23, 2025
· release notes
Workers AI adds /ai/tomarkdown/supported API endpoint to list supported file formats
New Robots.txt tab for tracking crawler compliance
Oct 21, 2025
· release notes
New Robots.txt tab in AI Crawl Control monitors crawler compliance and health
Schedule DNS policies from the Zero Trust dashboard using preset or custom time ranges.
Adds Preset Schedules (Business Hours, School Days, Weekends) as built-in templates for recurring policy activation in the Zero Trust dashboard Adds Custom Schedules allowing definition of specific days and up to three non-overlapping time ranges per day for policy enforcement Adds Timezone Control to enforce scheduled policies in a specific timezone or based on each user's local time Enables combined use of Schedule and Duration where duration expiration takes precedence over schedule times
4 details in Everything
New detections released for WAF managed rulesets
Oct 17, 2025
· release notes
Cloudflare WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. SQLi SQLi An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does. SSTI SSTI Server-Side Template Injection, a vulnerability class where attacker-controlled input is evaluated by a server-side template engine, enabling remote code execution or data exfiltration.
Adds SSTI - Arithmetic Probe detections across URI, header, and body fields for Server-Side Template Injection
1 detail in Everything
New Application Security reports (Closed Beta)
Oct 17, 2025
· release notes
New Application Security reports added to Security Center dashboard for Enterprise zones.
Adds Application Security report to the Security Center dashboard in Closed Beta. Enables monthly cyber security insights trends across all Enterprise zones in a Cloudflare account. Provides industry benchmark comparisons against peers in your industry.
3 details in Everything
Increased HTTP header size limit to 128 KB
Oct 16, 2025
· release notes
Cloudflare CDN CDN A content delivery network, servers distributed across locations that cache and serve content near readers. It can reduce loading time and traffic to the original server.
Increases the maximum supported size for both Cloudflare CDN request and response headers from 32 KB to 128 KB
1 detail in Everything
WARP client for macOS (version 2025.9.173.1)
Oct 16, 2025
· release notes
WARP macOS adds PMTUD support and unstable network status in GUI GUI A graphical user interface, controls such as windows, buttons and menus. It lets people use software visually rather than entering commands.
Adds Path Maximum Transmission Unit Discovery (PMTUD) to dynamically adjust packet sizing for optimized connection performance Adds a new GUI connection status message to indicate when the local network connection may be unstable
2 details in Everything
Monitor Groups for Advanced Health Checking With Load Balancing
Oct 16, 2025
· release notes
Cloudflare Load Balancing introduces Monitor Groups to combine multiple health monitors for sophisticated availability checks and smarter failover.
Adds Monitor Groups via the API to combine multiple health monitors (e.g., HTTP, TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. Adds monitoring only flag to isolate monitors from affecting pool health status while still receiving alerts and data.
2 details in Everything
WARP client for Windows (version 2025.9.173.1)
Oct 16, 2025
· release notes
Windows WARP client adds PMTUD for dynamic MTU optimization and GUI GUI A graphical user interface, controls such as windows, buttons and menus. It lets people use software visually rather than entering commands.
Adds Path Maximum Transmission Unit Discovery (PMTUD) to dynamically adjust packet sizing and optimize connection performance. Adds a new GUI connection status message to inform users when the local network connection may be unstable.
2 details in Everything
Single sign-on now manageable in the user experience
Oct 14, 2025
· release notes
SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management.
Adds new dashboard path Manage account > Members > Settings to manage SSO configuration without API access
1 detail in Everything
Enhanced AI Crawl Control metrics with new drilldowns and filters
Oct 14, 2025
· release notes
New drilldown filters and CSV export for AI Crawl Control metrics
Adds By Crawler , By Category , By Operator , By Host , and By Status Code grouping tabs to the AI Crawl Control Metrics view. Adds the Download CSV button to export filtered AI crawler activity data including applied filters and groupings. Adds referrer analytics for top traffic sources driving traffic to your site (Paid plans).
3 details in Everything
Worker startup time limit increased to 1 second
Oct 10, 2025
· release notes
Cloudflare Workers global scope startup limit raised from 400 ms to 1 second.
Allows Worker global scope to take up to 1 second to parse and execute, up from the previous 400 ms limit.
1 detail in Everything
Cloudflare Gateway adds three new domain categories: Keep Awake Software, Remote Access, and Shareware/Freeware.
Adds Keep Awake Software (ID 194) to the Technology parent category for DNS filtering.
1 detail in Everything
Expanded CT log activity insights on Cloudflare Radar
Oct 9, 2025
· release notes
New CT log stats (growth rate, counts, last update) added to Radar API and UI
Get Certificate Log Details API now returns log_growth_rate, included_certificate_count, eligible_for_inclusion_certificate_count, and last_update fields for Certificate Transparency Certificate Transparency A public, append-only log system maintained by various operators (Google runs several) that records every TLS certificate issued, letting anyone audit CAs for misissued or rogue certificates. Radar's CT log information page now displays log growth rate (certs/hour over 7 days), included certificate count, eligible-for-inclusion certificate count, and last update timestamp.
2 details in Everything
You can now deploy full-stack apps on Workers using Terraform
Oct 9, 2025
· release notes
Cloudflare Terraform provider v5.11.0 adds assets block to upload static assets with Workers.
Adds assets block to cloudflare_workers_script resource for static asset uploads Introduces beta cloudflare_worker_version resource to track Worker versions separately from state
2 details in Everything
New Overview Page for Cloudflare Workers
Oct 7, 2025
· release notes
Cloudflare Workers dashboard gains a new Overview Page with unified request, error, and binding management.
Adds a new Overview page in the Cloudflare dashboard for each Worker, serving as the default landing view with high-level metrics for requests, errors, and CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware.
1 detail in Everything
WARP client for macOS (version 2025.8.779.0)
Oct 7, 2025
· release notes
macOS WARP client GA release introduces MASQUE-only Proxy mode and L4 tunnel support.
WARP client for macOS is now Generally Available on the stable releases downloads page Proxy mode has been enhanced with custom congestion control optimizations over an L4 tunnel Proxy mode now supports SOCKS4, SOCK5, and HTTP CONNECT HTTP CONNECT An HTTP method that asks a proxy server to open a raw TCP tunnel to a target host, letting clients relay arbitrary traffic — including TLS — through the proxy without the proxy inspecting it. MASQUE protocol is now the only protocol that can use Proxy mode
4 details in Everything
└──▷ BREAKING ON UPGRADE
! Wireguard devices configured to use Proxy mode will lose connectivity unless a new WARP mode or the MASQUE protocol is selected.
WARP client for Linux (version 2025.8.779.0)
Oct 7, 2025
· release notes
Linux WARP client 2025.8.779.0 GA introduces MASQUE-only Proxy mode with doubled throughput
Proxy mode utilizes an L4 tunnel with custom congestion control optimizations, doubling throughput over L3 tunnels
1 detail in Everything
└──▷ BREAKING ON UPGRADE
! Devices using Proxy mode configured with WireGuard WireGuard A modern VPN protocol and Linux kernel module, maintained as an open-source project, that establishes encrypted tunnels using minimal code and fast cryptography, giving cyber tools a lightweight, high-performance transport layer. MASQUE protocol
WARP client for Windows (version 2025.8.779.0)
Oct 7, 2025
· release notes
Windows WARP client goes GA with MASQUE-only Proxy mode and doubled throughput.
Proxy mode now uses the MASQUE protocol exclusively over an L4 tunnel, replacing the previous L3 WireGuard WireGuard A modern VPN protocol and Linux kernel module, maintained as an open-source project, that establishes encrypted tunnels using minimal code and fast cryptography, giving cyber tools a lightweight, high-performance transport layer.
1 detail in Everything
└──▷ BREAKING ON UPGRADE
! If a device profile configured Proxy mode with WireGuard and you do not switch to a new WARP mode or the MASQUE protocol, devices matching that profile will lose connectivity.
New emergency WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. RCE RCE Remote code execution, the ability to run attacker-chosen code on another system through a vulnerability. Its impact depends on the permissions and access that code receives. command injection command injection An attack that makes an application execute operating-system commands supplied through untrusted input. It often happens when input is passed unsafely to a shell.
Adds Rule ID 100882 to detect missing authentication on Chaos Mesh controller endpoints. Adds Rule ID 100883 to block command injection via Chaos Mesh mutations. Adds Rule ID 100884 and 100888 to block additional Chaos Mesh command injection vectors (CVE-2025-59361, CVE-2025-59360). Adds Rule ID 100886 to block HTTP parameter pollution via form-data multipart boundaries. Adds Rule ID 100917 for generic SQLi SQLi An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does.
+1 more
show less
Adds Rule ID 100918 for generic SQLi information disclosure detection.
6 details in Everything
Browser Support Detection for PQ Encryption on Cloudflare Radar
Oct 6, 2025
· release notes
Cloudflare Radar adds browser detection for Post-quantum Post-quantum Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA.
The Post-quantum encryption card now checks whether a user’s browser supports post-quantum encryption and displays the key agreement in use if supported.
1 detail in Everything
R2 Data Catalog table-level compaction
Oct 6, 2025
· release notes
R2 Data Catalog adds wrangler r2 bucket catalog compaction enable subcommand for per-table Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS.
One-click Cloudflare Access for Workers
Oct 3, 2025
· release notes
One-click enablement of Cloudflare Access for Workers and Preview URLs directly from the Dashboard UI.
Adds Enable Cloudflare Access button on the Settings > Domains & Routes page for workers.dev and Preview URLs
1 detail in Everything
Workers Analytics Engine adds supports for new SQL functions
Oct 2, 2025
· release notes
Workers Analytics Engine adds new aggregate, bitwise, math, string, encoding, and type conversion SQL functions
argMin() returns the value associated with the minimum in a groupargMax() returns the value associated with the maximum in a grouptopK() returns an array of the most frequent values in a grouptopKWeighted() returns an array of the most frequent values in a group using weightsfirst_value() returns the first value in an ordered set of values within a partition
+23 more
show less
last_value() returns the last value in an ordered set of values within a partitionbitAnd() returns the bitwise AND of two expressionsbitCount() returns the number of bits set to one in the binary representation of a numberbitHammingDistance() returns the number of bits that differ between two numbersbitNot() returns a number with all bits flippedbitOr() returns the inclusive bitwise OR of two expressionsbitRotateLeft() rotates all bits in a number left by specified positionsbitRotateRight() rotates all bits in a number right by specified positionsbitShiftLeft() shifts all bits in a number left by specified positionsbitShiftRight() shifts all bits in a number right by specified positionsbitTest() returns the value of a specific bit in a numberbitXor() returns the bitwise exclusive-or of two expressionsabs() returns the absolute value of a numberlog() computes the natural logarithm of a numberround() rounds a number to a specified number of decimal placesceil() rounds a number up to the nearest integerfloor() rounds a number down to the nearest integerpow() returns a number raised to the power of another numberlowerUTF8() converts a string to lowercase using UTF-8 encodingupperUTF8() converts a string to uppercase using UTF-8 encodinghex() converts a number to its hexadecimal representationbin() converts a string to its binary representationtoUInt8() converts any numeric expression, or expression resulting in a string representation of a decimal, into an unsigned 8 bit integer
28 details in Everything
New Deepgram Flux model available on Workers AI
Oct 2, 2025
· release notes
Workers AI adds @cf/deepgram/flux speech-to-text model for voice agent streaming
Fine-grained Permissioning for Access for Apps, IdPs, & Targets now in Public Beta
Oct 2, 2025
· release notes
Cloudflare Access adds fine-grained RBAC RBAC Role-based access control, where permissions are assigned to roles such as reader or administrator and users receive those roles. It makes access easier to manage than individual permission lists.
Adds the ability to grant admin permissions to specific Access Applications . Adds the ability to grant admin permissions to individual Identity Providers . Adds the ability to grant admin rights to specific Targets .
3 details in Everything
Expanded File Type Controls for Executables and Disk Images
Oct 1, 2025
· release notes
Zero Trust Gateway now supports blocking dmg, pkg, msix, and appx file types in HTTP policies.
Adds dmg to the System category of File Type Controls for blocking Apple Disk Images Adds msix and appx to the Executable category for Microsoft Software Installers Adds pkg to the Executable category for Apple Software Packages
3 details in Everything
Cloudflare Containers introduces standard-4 instance type with up to 4 vCPU, 12 GiB memory, and 20 GB disk.
Adds standard-4 container instance type with 4 vCPU, 12 GiB memory, and 20 GB disk Increases standard-1 instance type disk capacity from 4 GB to 8 GB
2 details in Everything
New Confidence Intervals in GraphQL Analytics API
Oct 1, 2025
· release notes
GraphQL Analytics API adds confidence intervals for sampled sum/count fields
Adds confidence_level parameter to GraphQL queries on adaptive (sampled) datasets to return statistical ranges for sum and count fields. Supports confidence levels as decimals between 0 and 1 (e.g., 0.95) with a default of no intervals if omitted.
2 details in Everything
Application granular controls for operations in SaaS applications
Sep 30, 2025
· release notes
Cloudflare Gateway introduces Application Granular Controls for SaaS SaaS Software delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally.
Cloudflare Radar adds regional data via HTTP/NetFlows API endpoints and a new UI view.
Adds Get Geolocation and List Geolocations API endpoints to retrieve geo location data by geoId Adds adm1 dimension to all summary and timeseries_groups endpoints in HTTP and NetFlows for grouping by first level administrative division Adds geoId filter to all endpoints in HTTP and NetFlows to allow filtering by a specific administrative division Introduces a new Regional traffic insights page in the Radar UI for country-specific traffic views
4 details in Everything
SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management.
Extends SSO availability to all Cloudflare users (not just Enterprise) at no cost Adds direct API management of SSO configurations, removing the need to contact support
2 details in Everything
R2 Data Catalog now supports compaction
Sep 25, 2025
· release notes
R2 Data Catalog adds automatic compaction for Iceberg tables via CLI flag and UI setting
Adds wrangler r2 bucket catalog compaction enable subcommand to configure automatic compaction parameters. Enables automatic file compaction in R2 Data Catalog settings via the dashboard UI to improve query performance.
2 details in Everything
Run more Containers with higher resource limits
Sep 25, 2025
· release notes
Cloudflare raises concurrent Container limits: 400GiB RAM RAM Working memory that holds programs and data while a computer is running. Its contents usually disappear when power is removed.
Increases the memory limit for concurrent live Container instances to 400GiB (up from 40GiB). Increases the vCPU limit for concurrent live Container instances to 100 (up from 20). Increases the disk limit for concurrent live Container instances to 2TB (up from 100GB). Allows running 1000 concurrent dev instance type Containers. Allows running 400 concurrent basic instance type Containers.
+1 more
show less
Allows running 100 concurrent standard instance type Containers.
6 details in Everything
Adds Sign in with GitHub button as a new login option on the Cloudflare dashboard.
Refine DLP Scans with New Body Phase Selector
Sep 25, 2025
· release notes
Gateway HTTP DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest. Body Phase selector to scan only request or response bodies.
Adds the Body Phase selector in the Gateway HTTP policy builder to control which traffic direction is scanned. Enables Request Body scanning for user-initiated data exfiltration data exfiltration Moving data out of a system or organization without authorization. It can happen through network transfers, removable media or other channels. Enables Response Body scanning for inspecting file downloads and website content for sensitive data.
3 details in Everything
Cloudflare R2 now supports serverless SQL queries against Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS. wrangler r2 sql query command in open beta.
Introduces npx wrangler r2 sql query as a new CLI subcommand for executing distributed SQL queries against R2 Data Catalog tables. Adds support for querying Apache Iceberg tables managed by R2 Data Catalog using the wrangler toolkit.
2 details in Everything
Browser Rendering Playwright GA, Stagehand support (Beta), and higher limits
Sep 25, 2025
· release notes
Browser Rendering adds GA Playwright v1.55 support, Beta Stagehand automation, and tripled limits on paid plans.
Adds Generally Available support for Playwright v1.55 in Browser Run Adds Beta support for the Stagehand library to combine code with natural language instructions Tripling of execution limits for paid plans across REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
3 details in Everything
AI Search (formerly AutoRAG) now with More Models To Choose From
Sep 25, 2025
· release notes
AI Search now supports embedding embedding Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG.
Pipelines now supports SQL transformations and Apache Iceberg
Sep 25, 2025
· release notes
Cloudflare Pipelines adds SQL transformations and Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS.
└──▷ TRY IT
Initialize a new streaming pipeline from the command line to ingest and transform events.
copy
$ npx wrangler pipelines setup
Adds SQL transformation engine for stream processing in Cloudflare Pipelines Enables writing transformed data to R2 as Apache Iceberg tables via wrangler pipelines setup or dashboard Provides npx wrangler pipelines setup CLI command for pipeline initialization
3 details in Everything
Access Remote Desktop Protocol (RDP) destinations securely from your browser — now generally available!
Sep 22, 2025
· release notes
Cloudflare Access now GA for browser-based RDP RDP A Microsoft protocol that lets a user view and control a remote Windows desktop over a network, giving cyber tools a standard channel to audit, attack-simulate, or monitor Windows systems remotely. IPv6 IPv6 The current version of the Internet Protocol, standardized by the IETF, using 128-bit addresses to replace the exhausted IPv4 space. Cyber tools target it because modern networks run dual-stack or IPv6-only.
Browser-based RDP is generally available for all Cloudflare customers Added support for targets with IPv6 addresses Added Magic WAN as an on-ramp for browser-based RDP sessions Added WARP Connector as an on-ramp for browser-based RDP sessions Enhanced keyboard layout support for non-English languages (e.g., Portuguese, Chinese)
+2 more
show less
Improved handling of usernames containing spaces, quotes, or special characters Enhanced error messaging on the login page for RDP connection issues
7 details in Everything
New Metrics tab in AutoRAG for indexing health and endpoint usage comparison
Adds a Metrics tab to each AutoRAG instance to view indexing pipeline health Adds search breakdown metrics comparing usage between ai-search and search endpoints Adds top file retrievals data to identify frequently accessed files within the Metrics view
3 details in Everything
Cloudflare Workers ratelimit binding is now Generally Available and stable for production.
Stabilizes the ratelimit binding in Cloudflare Workers as the recommended interface for rate limiting logic
1 detail in Everything
Workers-rs v0.6.5 adds automatic panic recovery for Rust Workers via new Wasm Bindgen options.
Adds --experimental-reset-state-function compilation option to Wasm Bindgen to output __wbg_reset_state for VM state reset Enables automatic panic recovery for all new workers-rs deployments starting with version 0.6.5
2 details in Everything
Connect and secure any private or public app by hostname, not IP — with hostname routing for Cloudflare Tunnel
Sep 18, 2025
· release notes
Cloudflare Tunnel adds hostname-based routing for private and public apps
Adds hostname and domain routing for Cloudflare Tunnel, allowing routes to be defined by individual hostnames (e.g., payroll.acme.local) or entire domains (e.g., *.acme.local) instead of only IP addresses or CIDR CIDR A notation for a block of IP addresses, such as 10.0.0.0/24. The number after the slash says how many leading address bits identify the network. Enables precise egress control by routing traffic for public hostnames (e.g., bank.example.com) through a specific Tunnel to enforce a dedicated source IP.
2 details in Everything
Workers preview URLs now default to opt-in; existing affected Workers redirected until re-enabled.
Remote bindings GA - Connect to remote resources (D1, KV, R2, etc.) during local development
Sep 16, 2025
· release notes
Remote bindings GA allows local Workers to proxy D1, KV, R2 calls to deployed Cloudflare resources
remote binding config key (JSON/TOML) enables proxying local Worker bindings to deployed Cloudflare resourcesWrangler v4.37.0+ and Cloudflare Vite/Vitest plugins now support remote bindings without an experimental flag
2 details in Everything
DNS Firewall Analytics — now in the Cloudflare dashboard
Sep 16, 2025
· release notes
New interactive DNS Firewall analytics panels in Cloudflare dashboard.
Enables cross-panel filtering by dimensions including query name, query type, cluster, data center, protocol (UDP UDP A network protocol that sends individual messages without guaranteeing delivery or order. Applications trade built-in reliability for less overhead and can add their own recovery. TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. Provides access to 62 days of historical data with flexible intervals for trend analysis
2 details in Everything
New AI-Enabled Search for Zero Trust Dashboard
Sep 16, 2025
· release notes
Cloudflare introduces AI-powered search and Ask Cloudy agent in the Zero Trust Dashboard.
Adds AI-powered search for resources (applications, policies, device profiles), pages, and products within the Zero Trust Dashboard. Integrates Ask Cloudy , an AI agent trained on developer documentation and implementation guides, allowing users to ask configuration questions and receive recommendations while navigating between dashboard pages. Adds a new Find Recents tab under Zero Trust Overview displaying recent searches and Ask Cloudy history.
3 details in Everything
Log Explorer results table view gains column resizing, custom column selection, sorting, and value copying.
results_table in Log Explorer allows removing or adding columns to customize the displayed dataresults_table allows resizing columns for better data visibilityresults_table supports sorting columns by clicking headersresults_table enables copying values from any field directly
4 details in Everything
Log Explorer adds UI pivots for IP/JA3 JA3 A method for fingerprinting TLS clients by hashing fields from the ClientHello message, producing a short string that identifies the TLS library or application making a connection regardless of IP or port.
Adds right-click pivot from http_requests or fw_events IP Address or JA3 Fingerprint to Investigate portal Adds direct links from EdgeResponseStatus or OriginResponseStatus fields to documentation Adds click-to-link pivot from gateway_http policyid to Zero Trust Gateway policy settings
3 details in Everything
DNS filtering for private network onramps
Sep 11, 2025
· release notes
DNS filtering for private network onramps via new resolver IPs
Adds support for routing DNS traffic from Magic WAN and WARP Connector to Cloudflare Gateway using shared resolver IPs 172.64.36.1 and 172.64.36.2 Enables Source Internal IP as a valid traffic selector in resolver policies for private DNS routing to Internal DNS
2 details in Everything
Regional Email Processing for Germany, India, or Australia
Sep 11, 2025
· release notes
Adds Regional Email Processing locations (Germany, India, Australia) selectable during domain onboarding in Cloudflare Email security
Allows customers to select the email processing region (Germany, India, or Australia) for new domains via the UI when using MX, BCC, or Journaling onboarding methods. Enables automatic MX record updates from the UI when onboarding a domain managed by Cloudflare in Germany, India, or Australia.
2 details in Everything
D1 automatically retries read-only queries
Sep 11, 2025
· release notes
D1 automatically retries read-only SELECT/EXPLAIN/WITH queries with up to 2 attempts
Adds automatic retry logic for read-only queries (SELECT, EXPLAIN, WITH) on transient errors. Exposes total_attempts in the response metadata to indicate how many execution attempts occurred.
2 details in Everything
Agents SDK v0.1.0 and workers-ai-provider v2.0.0 with AI SDK v5 support
Sep 10, 2025
· release notes
Cloudflare Agents SDK v0.1.0 and workers-ai-provider v2.0.0 bring AI SDK v5 support with tool confirmation and message migration
Adds useAgentChat React hook for creating chat interfaces with automatic tool resolution Supports experimental_automaticToolResolution option in useAgentChat to auto-categorize tools by execution type Adds toolsRequiringConfirmation array argument to useAgentChat for manual tool confirmation lists Enables multi-part message handling with parts array including text and image types via sendMessage Provides isToolUIPart helper for detecting pending tool confirmations in message streams
+3 more
show less
Introduces automatic legacy message format migration within the SDK without code changes Updates workers-ai-provider to v2.0.0 for AI SDK v5 compatibility and enhanced file handling Adds support for serverExecuted: true flag in tool definitions to bypass client-side confirmation
8 details in Everything
Cloudflare has updated its Built with Cloudflare button to facilitate easier sharing of Cloudflare usage in project documentation.
Updates the Built with Cloudflare button to make it easier to share that you're building on Cloudflare
1 detail in Everything
Deploy static sites to Workers without a configuration file
Sep 9, 2025
· release notes
Wrangler now supports interactive deployment of static sites without a pre-existing configuration file via wrangler deploy [directory]
└──▷ USE IT
Deploy a static site immediately without setting up wrangler.jsonc first, letting CLI guide you through naming and config generation.
shell
copy
wrangler deploy dist
wrangler deploy [directory] or wrangler deploy --assets [directory] without an existing config triggers interactive prompts for project name, type, and compatibility dateAutomatically generates a wrangler.jsonc configuration file in the current directory to persist deployment settings
2 details in Everything
Cloudflare Magic WAN adds custom_ike_id via API for IPsec IPsec A suite of IETF protocols that authenticate and encrypt IP packets at the network layer, giving cyber tools a standards-based way to build VPNs or secure host-to-host tunnels without modifying applications.
Bidirectional tunnel health checks are compatible with all Magic on-ramps
Sep 5, 2025
· release notes
Magic on-ramps now accept bidirectional health checks from any tunnel in HA configs.
All Magic on-ramp devices accept bidirectional tunnel health check return packets regardless of which high-availability tunnel they traverse.
1 detail in Everything
Introducing EmbeddingGemma from Google on Workers AI
Sep 5, 2025
· release notes
Adds @cf/google/embeddinggemma-300m as a new embedding model embedding model Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. RAG RAG Retrieval-augmented generation: looking up relevant documents and adding them to the prompt before the model answers. It grounds responses in private or current data without retraining.
Enables selection of @cf/google/embeddinggemma-300m in the Generate Index step of the AI Search dashboard to support RAG pipelines across 100+ languages
1 detail in Everything
Increased static asset limits for Workers
Sep 4, 2025
· release notes
Workers static asset upload limit increased to 100,000 per version for paid/for-platforms plans
Paid and Workers for Platforms users can now upload up to 100,000 static assets per Worker version (previously 20,000) Wrangler v4.34.0+ required to utilize the new 100,000 asset limit; earlier versions enforce the 20,000 limit
2 details in Everything
A new, simpler REST API for Cloudflare Workers (Beta)
Sep 4, 2025
· release notes
New beta resource-oriented Workers API separates Worker, Version, and Deployment management with explicit endpoints
└──▷ USE IT
Define a Worker resource in Terraform to provision identity without uploading code immediately.
hcl
copy
resource "cloudflare_worker" "my_worker" {
account_id = "..."
name = "my-important-service"
}
Adds cloudflare_worker, cloudflare_worker_version, and cloudflare_workers_deployments resources to the Cloudflare Terraform provider (v5.9.0) for separate infrastructure and code lifecycle management
1 detail in Everything
Logging headers and cookies using custom fields
Sep 3, 2025
· release notes
Log Explorer now supports logging and filtering on header or cookie fields via custom fields in the http_requests dataset
Introducing new headers for rate limiting on Cloudflare's API
Sep 3, 2025
· release notes
Cloudflare REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Adds Ratelimit header to all Cloudflare REST API responses to expose remaining quota and reset time Adds Ratelimit-Policy header to define total quota and time window for each rate limit policy Adds Retry-After header on 429 errors to indicate seconds until capacity is available
3 details in Everything
Cloudflare introduces Email security Policy Admin role to allow policy management without full config access.
Cloudflare One WARP Diagnostic AI Analyzer
Aug 29, 2025
· release notes
Cloudflare One introduces a beta AI-driven diagnostic tool for WARP clients to automate root cause identification and troubleshooting guidance via the dashboard.
Cloudflare Terraform v5.9 adds cloudflare_snippet resource for snippet management.
cloudflare_zone_setting, cloudflare_worker_script, cloudflare_worker_route, and tiered_cache resources are stabilized
1 detail in Everything
New DEX MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Releases an MCP server for Digital Experience Monitoring (DEX) to expose device metrics via the Model Context Protocol Model Context Protocol Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Allows users to query connectivity and performance data for specific devices via natural language questions directed at the DEX API
2 details in Everything
Shadow IT - SaaS analytics dashboard
Aug 27, 2025
· release notes
New Shadow IT SaaS SaaS Software delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally.
Adds the Shadow IT - SaaS analytics dashboard to Cloudflare One Zero Trust Enables marking applications with approval statuses: Unreviewed , In Review , Approved , and Unapproved Allows using application approval statuses in Gateway HTTP policies
3 details in Everything
Deepgram and Leonardo partner models now available on Workers AI
Aug 27, 2025
· release notes
New Deepgram and Leonardo partner models plus WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output.
Adds @cf/deepgram/aura-1 (text-to-speech), @cf/deepgram/nova-3 (speech-to-text), and @cf/pipecat-ai/smart-turn-v2 (turn detection) models to Workers AI Adds @cf/leonardo/lucid-origin and @cf/leonardo/phoenix-1.0 text-to-image models to Workers AI
2 details in Everything
New CASB integrations for ChatGPT, Claude, and Gemini
Aug 26, 2025
· release notes
Cloudflare CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic. DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Adds ChatGPT (OpenAI) integration to Cloudflare CASB for agentless posture and DLP monitoring Adds Claude (Anthropic) integration to Cloudflare CASB for agentless posture and DLP monitoring Adds Gemini (Google) integration to Cloudflare CASB for agentless posture and DLP monitoring
3 details in Everything
List all vectors in a Vectorize index with the new list-vectors operation
Aug 26, 2025
· release notes
New list-vectors operation for Vectorize index
Manage and restrict access to internal MCP servers with Cloudflare Access
Aug 26, 2025
· release notes
Cloudflare Access now supports OAuth for internal MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds OAuth support for MCP server authentication within Cloudflare Access policies Enables self-hosted applications to delegate access to internal MCP servers via OAuth
2 details in Everything
Cloudflare introduces open beta MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Model Context Protocol Model Context Protocol Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds the ability to create MCP server portals that present multiple MCP servers on a single HTTP endpoint for agent access Introduces portal configuration to select specific tools and prompt templates per portal, enabling curated access for AI agents Enables Cloudflare Access authentication for the portal URL while supporting both unauthenticated and third-party/custom OAuth secured MCP servers
3 details in Everything
New DLP topic based detection entries for AI prompt protection
Aug 25, 2025
· release notes
Cloudflare Gateway DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Adds native detection and inspection for prompts submitted to Google Gemini, ChatGPT, Claude, and Perplexity via Prompt Detection for AI Applications Introduces topic classification for DLP engine evaluating Content (PII PII Personally Identifiable Information — data that can identify a specific individual, such as names, email addresses, or SSNs. Cyber tools flag or redact it to limit exposure and meet privacy regulations. Intent (Jailbreak attempts, requests for malicious code, attempts to extract PII) Provides five new predefined DLP profiles such as AI Prompt: AI Security and AI Prompt: PII Enables application granular controls in Gateway HTTP policies to apply DLP profiles to specific AI applications (e.g., ChatGPT) and actions (e.g., SendPrompt) Adds optional setting in Gateway policy to capture Full Prompt Logging and filter logs by conversation_id
5 details in Everything
Cloudflare Logpush gains support for delivery via fixed Aegis egress IPs.
Adds Aegis IP proxy zones to route Logpush traffic through a dedicated zone for fixed egress addresses Enables use of known, static source IPs for Logpush destinations to simplify firewall allowlisting
2 details in Everything
Audit logs (version 2) - Logpush Beta Release
Aug 22, 2025
· release notes
Cloudflare now supports sending Audit Logs v2 via Logpush beta.
Adds the Audit Logs v2 dataset as a source for Logpush jobs.
1 detail in Everything
New getByName() API to access Durable Objects
Aug 21, 2025
· release notes
Cloudflare Workers introduces the getByName() API for direct Durable Object access via name
Adds getByName() method to env.<DO_NAMESPACE> to retrieve a Durable Object client directly by its globally-unique name
1 detail in Everything
Gateway BYOIP Dedicated Egress IPs now available.
Aug 21, 2025
· release notes
Cloudflare Gateway now supports BYOIP BYOIP Bring Your Own IP — a cloud provider feature letting customers move their own publicly routable IP blocks into the provider's network, so traffic to those addresses routes through the cloud without renumbering.
Enterprise users can onboard their own IPv4 or IPv6 IPv6 The current version of the Internet Protocol, standardized by the IETF, using 128-bit addresses to replace the exhausted IPv4 space. Cyber tools target it because modern networks run dual-stack or IPv6-only. Adds a 'Use dedicated egress IPs (Cloudflare or BYOIP)' option and BYOIP dropdown to the Egress policies selection
2 details in Everything
Easier debugging in Workers with improved Wrangler error screen
Aug 19, 2025
· release notes
Wrangler error screen refreshed with youch engine, theme support, and better source map resolution.
└──▷ TRY IT
Debug Workers code locally with improved error visibility
copy
$ npx wrangler@latest dev
Adds youch-powered error screen to Wrangler's local development workflow for Workers debugging Adds light and dark theme support in the new Wrangler error UI
2 details in Everything
Subscribe to events from Cloudflare services with Queues
Aug 19, 2025
· release notes
Cloudflare adds event subscriptions via Queues to subscribe to account activity.
└──▷ USE IT
Subscribe an existing queue to R2 bucket creation events for automated processing.
shell
copy
npx wrangler queues subscription create my-queue --source r2 --events bucket.created
Adds wrangler queues subscription create CLI command to create event subscriptions Enables consuming events from R2, Workers KV, Workers AI, Workers Builds, Vectorize, Super Slurper, and Workflows
2 details in Everything
The Node.js and Web File System APIs in Workers
Aug 15, 2025
· release notes
Workers adds virtual filesystem support via node:fs module and Web File System API compatibility flags.
Adds node:fs module for ephemeral file read/write operations in Workers with nodejs_compat flag (default at date 2025-09-01) or enable_nodejs_fs_module compatibility flag. Adds disable_nodejs_fs_module compatibility flag to explicitly disable the node:fs module. Adds enable_web_file_system compatibility flag to expose the Web File System API in Workers without requiring nodejs_compat.
3 details in Everything
SFTP support for SSH with Cloudflare Access for Infrastructure
Aug 15, 2025
· release notes
SSH with Cloudflare Access for Infrastructure now allows SFTP SFTP SSH File Transfer Protocol, a file transfer standard built on top of SSH that provides encrypted upload, download, and remote file management; cyber tools use it to move files or exfiltrate data over an authenticated, encrypted channel.
Save time with bulk query creation in Brand Protection
Aug 15, 2025
· release notes
Cloudflare Brand Protection adds a bulk query creation API to create and save multiple queries in a single step
Steer Traffic by AS Number in Load Balancing Custom Rules
Aug 15, 2025
· release notes
Cloudflare adds AS Num field to Load Balancing Custom Rules for ASN ASN Autonomous System Number — a globally unique identifier assigned by regional internet registries to a network operator, letting routing protocols distinguish which organization controls a block of IP addresses.
AS Num added as a selectable Field in the Custom Rule UI within Cloudflare Load Balancing.
1 detail in Everything
Cloudflare Access Logging supports the Customer Metadata Boundary (CMB)
Aug 14, 2025
· release notes
Cloudflare Access Logging now respects Customer Metadata Boundary (CMB) configurations in logs.
Terraform provider improvements — Python Workers support, smaller plan diffs, and API SDK fixes
Aug 14, 2025
· release notes
Cloudflare Terraform provider adds Python Workers support, content_file/content_sha256 fields, and assets headers/redirects for Workers scripts.
Adds content_type = "text/x-python" to cloudflare_workers_script resource to deploy Python Workers (beta) in Terraform Provider 5.8.0 Adds content_file and content_sha256 fields to cloudflare_workers_script to store script content externally in Terraform Provider 5.7.0+ Adds assets.config.headers and assets.config.redirects support to cloudflare_workers_script resource for Asset headers and redirects in Terraform Provider 5.8.0
3 details in Everything
Python Workers handlers now live in an entrypoint class
Aug 14, 2025
· release notes
Python Workers handlers move to an entrypoint class; disable_python_no_global_handlers flag preserves old style
Adds WorkerEntrypoint class for defining Python Worker handlers in a structured way Supports disable_python_no_global_handlers compatibility flag to retain top-level handler definitions
2 details in Everything
Workers per-branch preview URLs now support long branch names
Aug 14, 2025
· release notes
Cloudflare Workers per-branch preview URLs now support long branch names via automatic truncation and hashing
wrangler@4.30.0 updates preview URL generation to handle branch names exceeding the 63-character DNS limit by appending a stable, unique hash.
1 detail in Everything
IBM Cloud Logs as Logpush destination
Aug 13, 2025
· release notes
Adds IBM Cloud Logs as a native Logpush destination for cloud security logs.
Adds HTTP Source Address and IBM API Key authentication fields to the Logpush configuration.
1 detail in Everything
Workers adds a minimal MessageChannel API for intra-Worker messaging via new compatibility flags.
Adds MessageChannel and MessagePort APIs at the global scope for Workers with compatibility date 2025-08-15 or later. Adds the expose_global_message_channel compatibility flag to enable the MessageChannel API. Adds the no_expose_global_message_channel compatibility flag to explicitly disable the MessageChannel API.
3 details in Everything
Introducing observability and metrics for Stream Live Inputs
Aug 8, 2025
· release notes
New broadcast health metrics available in Stream Live Input Dashboard details for observability.
Wrangler and the Cloudflare Vite plugin support `.env` files in local development
Aug 8, 2025
· release notes
Adds .env file support to wrangler dev and vite dev for local development environment variables
└──▷ USE IT
Override values for a specific local environment using an environment-specific .env file
shell
copy
wrangler dev --env staging
Supports .env files in project root to provide secrets and override environment variables during local development with Wrangler and the Cloudflare Vite plugin Supports .env.<environment-name> files (e.g. .env.staging) for multiple environments, merged when using wrangler <command> --env <environment-name> or CLOUDFLARE_ENV=<environment-name> vite dev
2 details in Everything
Directly import `waitUntil` in Workers for easily spawning background tasks
Aug 8, 2025
· release notes
Cloudflare Workers now supports direct import of waitUntil from cloudflare:workers for background tasks
Adds waitUntil as a named export from the cloudflare:workers module to extend Worker execution beyond the request lifecycle without passing the ctx object through function arguments
1 detail in Everything
Cloudflare Email Link Isolation now applies to all links in messages of a specified disposition (Enterprise/PhishGuard).
Requests made from Cloudflare Workers can now force a revalidation of their cache with the origin
Aug 7, 2025
· release notes
Cloudflare Workers now support cache property on Request for forced origin revalidation
Certificate Transparency Insights in Cloudflare Radar
Aug 6, 2025
· release notes
Cloudflare Radar adds CT insights API endpoints and a dedicated UI page for certificate issuance trends
New /ct/timeseries API endpoint retrieves certificate issuance time series data. New /ct/summary/{dimension} API endpoint retrieves certificate distribution by dimension. New /ct/timeseries_groups/{dimension} API endpoint retrieves time series of certificate distribution by dimension. New /ct/authorities and /ct/authorities/{ca_slug} API endpoints list and detail certification authorities from CCADB. New /ct/logs and /ct/logs/{log_slug} API endpoints list and detail CT logs from the Google Chrome log list.
+1 more
show less
Radar now includes a new Certificate Transparency Certificate Transparency A public, append-only log system maintained by various operators (Google runs several) that records every TLS certificate issued, letting anyone audit CAs for misissued or rogue certificates.
6 details in Everything
Cloudflare Sandbox SDK adds streaming, code interpreter, Git support, process control and more
Aug 5, 2025
· release notes
Cloudflare Sandbox SDK adds streaming code execution, Git support, process control, and port exposure
Adds createCodeContext function to create persistent Python, JavaScript, or TypeScript code execution contexts Adds runCode method with onStdout and onResult streaming callbacks for real-time output processing Adds runCodeStream function for returning a direct streaming response from code execution Adds rich output support (text, html, png, svg, json, chart) for interpreter results Adds Git integration via gitCheckout method to clone repositories into the sandbox file system
+2 more
show less
Adds startProcess, listProcesses, getProcess, killProcess, killAllProcesses, and streamProcessLogs methods for full background process lifecycle control Adds exposePort method to generate public preview URLs for services running on specific ports inside the sandbox
7 details in Everything
OpenAI open models now available on Workers AI
Aug 5, 2025
· release notes
Workers AI adds Day 0 support for OpenAI gpt-oss-120b and gpt-oss-20b models with Responses API via new /responses endpoint
Agents SDK adds MCP Elicitation support, http-streamable support, task queues, email integration and more
Aug 5, 2025
· release notes
Agents SDK gains MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds elicitInput() method to request user input during tool execution with durable state preservation Adds http-streamable transport support for MCP via the new default export serve signature Adds .queue() method to Agent class for lightweight background task deferral Adds onEmail lifecycle method and EmailAgent base class for automatic email processing Enables automatic context wrapping so getCurrentAgent() works inside RPC RPC Remote Procedure Call, a protocol that lets a program execute a function on another machine as if it were local, giving cyber tools a structured way to communicate across processes or hosts without managing raw sockets.
5 details in Everything
Develop locally with Containers and the Cloudflare Vite plugin
Aug 1, 2025
· release notes
Adds containers configuration and new APIs to develop Cloudflare Workers with Containers locally via Vite
Adds containers section in Wrangler config for local development with the Cloudflare Vite plugin.
1 detail in Everything
Terraform V5 support for tunnels and routes
Jul 31, 2025
· release notes
Cloudflare Terraform provider updates Cloudflare WAN tunnels and routes resources for Terraform provider version 5 compatibility.
Magic Transit and Magic WAN health check data is fully compatible with the CMB EU setting.
Jul 30, 2025
· release notes
Magic Transit and Magic WAN health check data is now accessible for accounts with CMB EU enabled via GraphQL API.
magicTransitTunnelHealthChecksAdaptiveGroups and magicTransitTunnelTrafficAdaptiveGroups GraphQL endpoints are compatible with the CMB EU setting.Access to GRE GRE A tunneling protocol that wraps one network packet inside another, letting tools carry arbitrary traffic across IP networks without modifying the payload, useful for traffic capture and network emulation. IPsec IPsec A suite of IETF protocols that authenticate and encrypt IP packets at the network layer, giving cyber tools a standards-based way to build VPNs or secure host-to-host tunnels without modifying applications.
2 details in Everything
Deploy to Cloudflare buttons now support Worker environment variables, secrets, and Secrets Store secrets
Jul 29, 2025
· release notes
Deploy to Cloudflare buttons now support passing Worker environment variables, secrets, and Secrets Store secrets during deployment
Deploy to Cloudflare button templates can now include vars, secrets, and secrets_store_secrets definitions in Wrangler config (wrangler.toml or package.json) so these values are presented to users during the dashboard deployment flow.Support for defining secrets_store_secrets (with binding, store_id, and secret_name fields) in Wrangler configuration files within deployable templates.
2 details in Everything
Audit logs (version 2) - UI Beta Release
Jul 29, 2025
· release notes
Audit Logs v2 UI beta introduces advanced filtering, JSON view, and infinite scroll for account activity investigation
Adds Manage Account > Audit Logs navigation to access the new Audit Logs v2 user interface Adds advanced filtering by actor, resource, and method in the Audit Logs v2 UI Adds on-hover filter controls to include or exclude values directly from log entries Adds detailed log sidebar for rich context without leaving the main view Adds JSON log view to inspect raw log data in structured format
+2 more
show less
Adds custom time range selection for historical activity views Adds infinite scroll for seamless browsing of audit logs
7 details in Everything
Gateway HTTP Filtering on all ports available in open BETA
Jul 24, 2025
· release notes
Cloudflare Gateway HTTP filtering now applies to non-standard ports in open beta.
Adds Inspect on all ports setting to apply A/V scanning, DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest. sandboxing sandboxing Running code inside a restricted environment that limits what it can access or change. The isolation reduces the impact of mistakes or untrusted code, depending on the sandbox's controls. Expands Gateway filtering surface beyond standard HTTP (80) and HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate.
2 details in Everything
Test out code changes before shipping with per-branch preview deployments for Cloudflare Workers
Jul 22, 2025
· release notes
Per-branch preview URLs for Cloudflare Workers via Git integration and Wrangler CLI
└──▷ TRY IT
Upload a Worker version with a custom, memorable preview alias via the CLI.
copy
$ wrangler versions upload --preview-alias staging
Auto-generates stable branch preview URLs on GitHub/GitLab pull requests so changes can be tested before merging Posts Commit Preview URL (commit-specific) and Branch Preview URL (branch-stable alias) as PR comments Adds --preview-alias flag to wrangler versions upload for custom preview alias names
3 details in Everything
Audio mode for Media Transformations
Jul 22, 2025
· release notes
Cloudflare Media Transformations now supports audio mode for extracting M4A audio from video sources.
└──▷ TRY IT
Extract a 60-second audio clip starting at 3 seconds from a video for use in downstream AI inference workflows.
copy
$ https://example.com/cdn-cgi/media/mode=audio,time=3s,duration=60s/<input video with diction>
Adds mode=audio parameter to Media Transformations API endpoints, enabling extraction of audio from video sources into M4A format. Adds time and duration parameters to mode=audio queries to control the start point and length of the extracted audio segment.
2 details in Everything
Subaddressing support in Email Routing
Jul 21, 2025
· release notes
Email Routing now supports RFC 5233 subaddressing (plus addressing), allowing dynamic context capture in the +detail part.
Adds support for + separator to augment custom Email Routing addresses with arbitrary detail information. Enables capturing +detail parts from email headers for tracking source or categorization in logs, Email Workers, or Agent applications.
2 details in Everything
Virtual Cloudflare One Appliance with KVM support (open beta)
Jul 21, 2025
· release notes
Virtual Cloudflare One Appliance now supports Proxmox VE in open beta for KVM KVM A Linux kernel module that turns the kernel into a hypervisor, letting a process run fully isolated virtual machines using hardware virtualisation extensions. Cyber tools use it to sandbox execution environments at near-native speed.
Adds support for deploying the Virtual Cloudflare One Appliance on Proxmox VE hypervisors Enables connecting branch or data center networks to Cloudflare WAN without dedicated hardware via the new KVM appliance option
2 details in Everything
New Brand Protection API endpoints for creating/deleting queries and downloading matches
Adds the Brand Protection API to Security Center, enabling creation of new string or logo queries via a new REST endpoint.
1 detail in Everything
Cloudflare Terraform provider v5.7.0 stabilizes the v5 release by adding new infrastructure management resources and fixing critical state drift issues.
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. XSS XSS Cross-site scripting, an attack that runs malicious script in another user's browser through a trusted site. It can steal data or perform actions using the user's session.
Adds detection for XSS via HTML attribute overloading (Rule ID 2aa3d845, legacy 100798) to the Cloudflare Managed Ruleset, changing action from Log to Block Adds detection for XSS via onToggle event abuse on elements like <details> (Rule ID 37548d06, legacy 100799) to the Cloudflare Managed Ruleset, changing action from Log to Block
2 details in Everything
New onboarding guides for Zero Trust
Jul 10, 2025
· release notes
Cloudflare Zero Trust adds eight new onboarding guides in the dashboard Get Started tab
Adds a Get Started tab to the Zero Trust dashboard containing walkthroughs for setting up common use cases end-to-end. Includes eight specific onboarding flows: Securely access a private network, Device-to-device / mesh networking, Network to network connectivity, Secure web traffic, Secure DNS for networks, Clientless web access, Clientless SSH access, and Clientless RDP RDP A Microsoft protocol that lets a user view and control a remote Windows desktop over a network, giving cyber tools a standard channel to audit, attack-simulate, or monitor Windows systems remotely.
2 details in Everything
Log Explorer now surfaces monthly ingestion metrics to the top of Log Search and Manage Datasets screens.
Monthly usage is displayed at the top of the Log Search screen in Log Explorer to help customers monitor data ingestion volume for billing. Monthly usage is displayed at the top of the Manage Datasets screen in Log Explorer to help customers monitor data ingestion volume for billing.
2 details in Everything
Faster indexing and new Jobs view in AutoRAG
Jul 8, 2025
· release notes
AutoRAG Jobs view and faster indexing allow monitoring sync status and logs directly in Cloudflare dashboard.
Adds a new Jobs view in the AutoRAG UI to monitor indexing progress and history
1 detail in Everything
Cloudflare Images now ingests HEIC input format and serves AVIF AVIF An open image format based on the AV1 video codec, maintained by the Alliance for Open Media, offering smaller file sizes than JPEG or PNG at comparable quality — useful when a tool serves image-heavy web interfaces.
Cloudy summaries for Access and Gateway Logs
Jul 7, 2025
· release notes
Cloudflare adds AI-powered summaries to Access and Gateway block logs via Cloudy agent
New App Library for Zero Trust Dashboard
Jul 7, 2025
· release notes
Cloudflare adds App Library for Zero Trust Dashboard to visualize SaaS SaaS Software delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally. CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic.
Adds App Library UI section under My Team for comprehensive visibility of SaaS applications used in Gateway policies, CASB integrations, and Access for SaaS. Enables tracking of usage across your organization to understand user behavior for individual Applications within the App Library.
2 details in Everything
Hyperdrive now supports configuring the amount of database connections
Jul 3, 2025
· release notes
Hyperdrive now supports configuring the database connection count for your origin database.
Adds configurable database connection pool size to Hyperdrive configurations, with a minimum of 5 connections.
1 detail in Everything
Access RDP securely from your browser — now in open beta
Jul 1, 2025
· release notes
Cloudflare Access open beta for browser-based RDP RDP A Microsoft protocol that lets a user view and control a remote Windows desktop over a network, giving cyber tools a standard channel to audit, attack-simulate, or monitor Windows systems remotely. SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone.
Adds open beta support for Browser-based RDP via Cloudflare Access. Enables access recording to track user server access for compliance.
2 details in Everything
Enhanced support for static assets with the Cloudflare Vite plugin
Jul 1, 2025
· release notes
Cloudflare Vite plugin adds automatic client build output for Worker asset URLs and static asset imports in Workers
Enables import of static assets as URLs, strings, from the public directory, and inlining within Workers
1 detail in Everything
Bot & Crawler Insights in Cloudflare Radar
Jul 1, 2025
· release notes
New /bots/ and /bots/crawlers/ API endpoints add bot activity visibility to Cloudflare Radar.
Adds /bots/ endpoint to list all bots tracked by Radar Adds /bots/{bot_slug} endpoint to retrieve detailed metadata for a specific bot Adds /bots/timeseries endpoint for time-series data on bot activity Adds /bots/summary/{dimension} endpoint for overview of bot HTTP request distributions Adds /bots/timeseries_groups/{dimension} endpoint for time-series data on bot request distributions by dimension
+4 more
show less
Adds /bots/crawlers/summary/{dimension} endpoint for crawler HTTP request distribution overviews Adds /bots/crawlers/timeseries_groups/{dimension} endpoint for crawler request time-series data Supports filtering bots by bot, bot_operator, and bot_category parameters Supports crawler analysis dimensions: user_agent, referer, and crawl_refer_ratio
9 details in Everything
└──▷ BREAKING ON UPGRADE
! The previously available verified_bots endpoints are deprecated in favor of the new bot insights APIs
Redesigned UI adds dedicated AI Crawlers and Metrics tabs for granular control of AI crawler activity.
Adds new AI Crawlers tab in the dashboard to block specific AI crawlers Adds new Metrics tab to view AI Crawl Control metrics
2 details in Everything
Introducing Pay Per Crawl (private beta)
Jul 1, 2025
· release notes
Introduces Pay Per Crawl private beta allowing site owners to monetize AI crawler access via Stripe and pricing controls.
Adds Pay Per Crawl feature enabling site owners to set pricing and select which AI crawlers to charge for content access Allows management of AI crawler payments via Stripe integration within AI Crawl Control Provides analytics monitoring on successful content deliveries from charged AI crawlers
3 details in Everything
Graceful withdrawal of BYOIP prefixes
Jun 30, 2025
· release notes
Cloudflare Magic Transit now supports AS prepending for BYOIP BYOIP Bring Your Own IP — a cloud provider feature letting customers move their own publicly routable IP blocks into the provider's network, so traffic to those addresses routes through the cloud without renumbering.
Remote bindings (beta) now works with Next.js — connect to remote resources (D1, KV, R2, etc.) during local development
Jun 30, 2025
· release notes
Cloudflare extends its remote bindings beta to Next.js developers, allowing local development sessions to interact with live D1, KV, and R2 resources via the @opennextjs/cloudflare adapter.
Mail authentication requirements for Email Routing
Jun 30, 2025
· release notes
Email Routing now enforces SPF SPF An email authentication standard that lets a domain owner publish, via DNS, which mail servers are authorized to send on its behalf, so receiving servers can reject spoofed senders. DKIM DKIM An email authentication standard that lets a sending mail server cryptographically sign outgoing messages so receiving servers can verify the signature was not forged or tampered with in transit.
└──▷ BREAKING ON UPGRADE
! Emails sent to Cloudflare Email Routing without valid SPF or DKIM signatures will fail to forward after July 3, 2025.
Cloudflare One Agent for iOS (version 1.11)
Jun 30, 2025
· release notes
Cloudflare One Agent for iOS 1.11 adds post-quantum cryptography post-quantum cryptography Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA.
Adds post-quantum cryptography support to the WARP tunnel for enabled devices Includes DNS over HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate.
2 details in Everything
Cloudflare One Agent for Android (version 2.4.2)
Jun 30, 2025
· release notes
Cloudflare One Agent for Android 2.4.2 adds default DoH DoH DNS over HTTPS, an IETF standard (RFC 8484) that tunnels DNS queries inside encrypted HTTPS traffic, making resolution indistinguishable from web traffic and bypassing traditional DNS-based monitoring. post-quantum cryptography post-quantum cryptography Cryptography designed to stay secure against a large quantum computer, which could break today's RSA and elliptic-curve keys. NIST standardized the first algorithms in 2024 as ML-KEM, ML-DSA and SLH-DSA.
Adds Enable qlogs toggle under Settings > Advanced > Diagnostics > Debug Logs to control QLog generation Includes DNS over HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! The QLog setting from previous releases is no longer respected; use the new Enable qlogs toggle instead.
Run and connect Workers in separate dev commands with the Cloudflare Vite plugin
Jun 26, 2025
· release notes
Cloudflare Vite plugin enables running and connecting Workers across separate dev commands.
└──▷ TRY IT
Run a Worker using the Vite plugin in one terminal while developing another Worker locally in a second terminal.
copy
$ # Terminal 1
vite dev
# Terminal 2
wrangler dev
Adds the ability to run and connect Workers in separate dev commands via the Cloudflare Vite plugin Supports service bindings and tail consumers between vite dev and wrangler dev instances
2 details in Everything
Run AI-generated code on-demand with Code Sandboxes (new)
Jun 25, 2025
· release notes
Cloudflare introduces Code Sandboxes, enabling Workers to execute untrusted code in isolated container-like environments.
getSandbox() and Sandbox from the new @cloudflare/sandbox module allow Workers to spawn isolated execution environments for running AI-generated or untrusted code safely.
1 detail in Everything
@cloudflare/actors library - SDK for Durable Objects in beta
Jun 25, 2025
· release notes
@cloudflare/actors library beta introduces Actor class, storage helpers, and alarm scheduling for Durable Objects.
Introduces the new @cloudflare/actors SDK package in beta for building applications on Durable Objects. Adds a named Actor class pattern that allows accessing Durable Objects without manually writing the communicating Worker, with default routing to a default DO name. Exposes a static nameFromRequest method on the Actor class for routing requests to specific Durable Objects by name. Adds Storage helper class imported from @cloudflare/actors/storage for querying embedded SQLite and managing SQL schema migrations. Includes alarm helpers within the SDK for scheduling multiple alarms using dates, delays in seconds, or cron expressions.
5 details in Everything
Data Security Analytics in the Zero Trust dashboard
Jun 23, 2025
· release notes
Cloudflare Zero Trust now provides a Data Security Analytics dashboard in the Insights section, enabling security teams to track sensitive data movement trends and inventory stored data across SaaS SaaS Software delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally.
CNI v1 dataplane customers can now subscribe to maintenance alert emails.
Increased blob size limits in Workers Analytics Engine
Jun 20, 2025
· release notes
Cloudflare Workers Analytics Engine increases blob field size limit from 5 KB to 16 KB
Increases the maximum total size of blobs fields in data points written via writeDataPoint from 5 KB to 16 KB
1 detail in Everything
Automate Worker deployments with a simplified SDK and more reliable Terraform provider
Jun 19, 2025
· release notes
Cloudflare SDKs add simplified programmatic Worker deployment interface
cloudflare-typescript (4.4.1) and cloudflare-python (4.3.1) add a structured object interface for programmatic Worker deployments that replaces manual multipart/form-data construction.client.workers.scripts.update() method accepts a metadata object with main_module, bindings, and compatibility_date alongside a files map, handled automatically by the SDK.
2 details in Everything
View custom metadata in responses and guide AI-search with context in AutoRAG
Jun 19, 2025
· release notes
AutoRAG now returns custom metadata in search responses and supports a context field to guide LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code.
Returns object custom_metadata inside the attributes > file section of /search and /ai-search response payloads Supports passing an optional context field in object custom metadata to provide additional guidance for AI-generated answers
2 details in Everything
Account-level DNS analytics now available via GraphQL Analytics API
Jun 19, 2025
· release notes
Account-level DNS analytics now available via GraphQL Analytics API
Filter your AutoRAG search by file name
Jun 19, 2025
· release notes
AutoRAG now supports filename attribute filtering for precise search control
Adds filename filter attribute to AutoRAG search queries
1 detail in Everything
Remote bindings public beta - Connect to remote resources (D1, KV, R2, etc.) during local development
Jun 18, 2025
· release notes
Cloudflare adds wrangler dev --x-remote-bindings and experimental_remote to allow local Workers to connect to deployed D1, KV, R2 resources
└──▷ TRY IT
Test local code against real production R2 data without redeploying.
copy
$ wrangler dev --x-remote-bindings
Adds the --x-remote-bindings flag to wrangler dev to enable proxying binding calls to deployed Cloudflare resources during local development. Introduces the experimental_remote boolean field in wrangler.toml or package.json bindings to enable remote access for specific D1, KV, or R2 bindings. Enables integration with the Cloudflare Vite Plugin and Vitest Plugin for remote binding support in development workflows.
3 details in Everything
Cloudflare Log Explorer GA: native log search with natural language charts, saved queries, and account/zone level access.
Enables Log Explorer in the Cloudflare dashboard for native observability and forensics of traffic logs. Adds natural language chart definition for custom dashboards measuring response time, error rates, and more. Adds Log Search with data type-aware filters and custom SQL support for detailed log investigation. Adds the ability to save and share Log Search queries with other users in the account. Enables Log Explorer access at both the account and zone level.
5 details in Everything
Gateway will now evaluate Network policies before HTTP policies from July 14th, 2025
Jun 18, 2025
· release notes
Cloudflare Gateway changes policy evaluation order: Network policies now evaluated before HTTP policies.
Gateway evaluates Network (Layer 4) policies before HTTP (Layer 7) policies, changing the enforcement sequence from DNS→HTTP→Network to DNS→Network→HTTP.
1 detail in Everything
└──▷ BREAKING ON UPGRADE
! Block notifications for domains blocked by both HTTP and Network policies will now reflect the Network policy's notification setting (or silence), as the Network policy triggers first.
Control which routes invoke your Worker script for Single Page Applications
Jun 17, 2025
· release notes
Wrangler v4.20+ supports run_worker_first array in assets config for granular SPA routing.
Adds support for an array of route patterns in the run_worker_first config key within .wrangler/config/toml or wrangler.json to control which routes invoke a Worker script for Single Page Applications.
1 detail in Everything
Cloudflare Terraform v5.6.0 adds four new resources for schema validation and device settings
Adds cloudflare_schema_validation_operation_settings resource for managing schema validation operations Adds cloudflare_schema_validation_schemas resource for managing schema validation schemas Adds cloudflare_schema_validation_settings resource for managing schema validation settings Adds cloudflare_zero_trust_device_settings resource for managing zero trust device settings
4 details in Everything
Internal DNS (beta) now manageable in the Cloudflare dashboard
Jun 16, 2025
· release notes
Beta UI allows direct creation and management of Internal DNS zones and views in the Cloudflare dashboard
Grant account members read-only access to the Workers Platform
Jun 16, 2025
· release notes
Cloudflare adds a Workers Platform (Read-only) IAM IAM Identity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access.
Renames the existing Workers Admin role to Workers Platform Admin .
1 detail in Everything
Access git commit sha and branch name as environment variables in Workers Builds
Jun 10, 2025
· release notes
Workers Builds now injects CI, WORKERS_CI_COMMIT_SHA, and other env vars by default.
Adds automatic injection of CI, WORKERS_CI, WORKERS_CI_BUILD_UUID, WORKERS_CI_COMMIT_SHA, and WORKERS_CI_BRANCH environment variables during Workers Builds. Enables overriding injected defaults or adding custom environment variables via the Worker Settings page.
2 details in Everything
Match Workers subrequests by upstream zone — cf.worker.upstream_zone now supported in Transform Rules
Jun 9, 2025
· release notes
Cloudflare adds a new expression field to Transform Rules, enabling granular control over requests from Workers subrequests across zones.
└──▷ HOW TO FIND IT
Conditionally modify requests originating from Workers subrequests in a different zone.
📍 (cf.worker.upstream_zone != "" and cf.worker.upstream_zone != "myappexample.com")
More flexible fallback handling — Custom Errors now support fetching assets returned with 4xx or 5xx status codes
Jun 9, 2025
· release notes
Custom Errors now fetch assets from origins returning 4xx/5xx status codes
Cloudflare One Analytics Dashboards and Exportable Access Report
Jun 5, 2025
· release notes
Cloudflare introduces new analytics dashboards and exportable access reports in the Zero Trust dashboard.
Adds Cloudflare One Analytics Dashboards for centralized visibility into application access and network activity Adds an exportable Access Report to view high-level metrics and trends in application access
2 details in Everything
Performance and size optimization for the Cloudflare adapter for Open Next
Jun 5, 2025
· release notes
v1.2 of the Cloudflare adapter for Open Next reduces bundle size and improves startup performance.
New Account-Level Load Balancing UI and Private Load Balancers
Jun 4, 2025
· release notes
New centralized Account-Level Load Balancing UI and Private Load Balancers for private network traffic management.
Adds centralized Account-Level Load Balancing UI to view, configure, and monitor all load balancers across every zone in an account from a single interface. Introduces Private Load Balancers to distribute traffic to applications hosted within private networks via WARP & Magic WAN integration.
2 details in Everything
Improved onboarding for Shopify merchants
Jun 3, 2025
· release notes
Cloudflare adds automatic Onboarding for Online (O2O) to Shopify merchants with checkout protection and branded DNS records
Enables automatic Cloudflare O2O onboarding for all mutual Shopify customers without manual support intervention Displays a Shopify logo with helpful tooltips in DNS records for merchants Blocks Workers and Snippets from running on the checkout path to reduce risk and improve security
3 details in Everything
View an architecture diagram of your Worker directly in the Cloudflare dashboard
Jun 3, 2025
· release notes
New Bindings tab in Cloudflare dashboard visualizes and allows modifying Worker architecture diagrams.
Adds the Bindings tab to any Workers application in the Cloudflare dashboard, providing a visual diagram of the architecture and support for adding and managing bindings directly from the interface.
1 detail in Everything
AI Gateway adds OpenAI compatible endpoint
Jun 3, 2025
· release notes
Cloudflare AI Gateway adds an OpenAI-compatible endpoint for provider switching via baseURL and model parameters.
Adds OpenAI Compatible endpoint support to AI Gateway, enabling the use of standard OpenAI SDK formats with any backend provider Enables provider switching by configuring the model and apiKey parameters in the client instance
2 details in Everything
Cloudflare User Groups & Enhanced Permission Policies are now in Beta
Jun 2, 2025
· release notes
Cloudflare launches Beta for User Groups, SCIM SCIM A standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave. IAM IAM Identity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access.
Adds the User Groups IAM primitive for creating collections of account members with inherited permission policies, creatable via API Introduces SCIM User Groups beta to sync memberships directly from upstream identity providers identity providers A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. Entra ID Entra ID Microsoft's cloud-based identity and access management service, formerly Azure Active Directory, used by cyber tools to authenticate users and enforce access policies in Microsoft 365 and Azure environments. Visually overhauls the Permission Policies UI to improve definition of role-based access for specific principals
3 details in Everything
Debug, profile, and view logs for your Worker in Chrome Devtools — now supported in the Cloudflare Vite plugin
May 30, 2025
· release notes
The Cloudflare Vite plugin now supports debugging Workers via Chrome Devtools.
Adds support for debugging, profiling, and viewing logs for a Worker in Chrome Devtools when using the Cloudflare Vite plugin Exposes a Debug URL (e.g., http://localhost:5173/__debug) in the console when running vite to launch Chrome Devtools connected to the local Worker
2 details in Everything
Fine-tune image optimization — WebP now supported in Configuration Rules
May 30, 2025
· release notes
WebP format now supported as a value for the Polish setting in Configuration Rules
New Gateway Analytics in the Cloudflare One Dashboard
May 29, 2025
· release notes
New Gateway Analytics dashboards in the Cloudflare One Dashboard provide visibility into DNS, HTTP, and Network sessions.
Adds a new Analytics section to the Cloudflare Zero Trust dashboard side navigation for visualizing Gateway traffic patterns, top users, security actions, and geographic regions.
1 detail in Everything
Playwright MCP server is now compatible with Browser Rendering
May 28, 2025
· release notes
Playwright MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface.
Adds createMcpAgent function to @cloudflare/playwright-mcp that accepts env.BROWSER to enable Browser Rendering integration Enables AI-driven browser automation (screenshots, form filling, scraping) via the Playwright MCP server on Cloudflare Workers
2 details in Everything
Gateway Protocol Detection Now Available for Pay-as-you-go and Free Plans
May 27, 2025
· release notes
Protocol detection logging and filtering now available for Pay-as-you-go and Free plans.
Increased limits for Cloudflare for SaaS and Secrets Store free and Pay-as-you-go plans
May 27, 2025
· release notes
Cloudflare raises custom hostname and Secrets Store limits for SaaS SaaS Software delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally.
New GraphQL Analytics API Explorer and MCP Server
May 23, 2025
· release notes
Cloudflare adds in-browser GraphQL Analytics API Explorer and MCP Server MCP Server A process that exposes tools, resources, and prompts over Anthropic's Model Context Protocol, letting an AI agent call external APIs or local services through a standardised interface.
Adds the GraphQL API Explorer, a browser-based interface for building and running GraphQL Analytics queries with OAuth authentication Adds the GraphQL MCP Server to enable natural language interaction with the GraphQL Analytics API
2 details in Everything
New Applications Added to Zero Trust
May 18, 2025
· release notes
Cloudflare Zero Trust adds 42 new applications (33 AI, others HR/Dev/Sales) for Gateway policy enforcement via App Library
Durable Objects are now supported in Python Workers
May 16, 2025
· release notes
Python Workers now support creating and binding Durable Objects for stateful applications
Adds the DurableObject class to the Python workers module, enabling stateful compute with storage in Python Workers.
1 detail in Everything
Open email attachments with Browser Isolation
May 15, 2025
· release notes
Email attachments can now be viewed safely in a remote browser via the new Attachments section in Zero Trust
Adds an Attachments section to email messages displaying classifications like Malicious, Suspicious, Encrypted and a Browser Isolation icon for clientless viewing Requires enabling 'Allow users to open a remote browser without the device client' in Zero Trust settings and assigning Browser Isolation (BISO) seats
2 details in Everything
Cloudflare Gateway Domain Categories adds Ads, Finance, Brokerage, Security, and other category mappings.
Introducing Origin Restrictions for Media Transformations
May 14, 2025
· release notes
New origin restrictions for Media Transformations let admins whitelist domains for media fetching.
Adds source origin restrictions to Media Transformations (beta) with a per-domain sources list in the Stream UI Defaults to allowing transformations only on images and video from the same domain as the transformation request
2 details in Everything
New Applications Added for DNS Filtering
May 13, 2025
· release notes
Cloudflare Gateway adds DNS policy support for 273 new applications to manage outbound traffic.
SAML HTTP-POST bindings support for RBI
May 13, 2025
· release notes
Remote Browser Isolation adds SAML SAML A standard for passing signed identity assertions between a sign-in provider and an application. It lets a user sign in through their organization's identity provider. IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems.
Adds SAML HTTP-POST bindings support for Remote Browser Isolation to enable seamless authentication for SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. Improves compatibility with multi-factor authentication multi-factor authentication Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone.
2 details in Everything
Cloudflare DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
More ways to match — Snippets now support Custom Lists, Bot Score, and WAF Attack Score
May 9, 2025
· release notes
Snippets and Cloud Connector now match on Custom Lists (IP/AS/Hostname), Bot Score, and WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Custom lists matching – Snippets and Cloud Connector now support user-created IP, AS, and Hostname lists via dashboard or Lists API . Great for shared logic across zones.Bot Score and WAF Attack Score – Use Cloudflare’s intelligent traffic signals to detect bots or attacks and take advanced, tailored actions with just a few lines of code.
2 details in Everything
Publish messages to Queues directly via HTTP
May 9, 2025
· release notes
Cloudflare Queues now supports direct HTTP publishing via a new POST endpoint.
Adds POST /client/v4/accounts/<account_id>/queues/<queue_id>/messages endpoint for direct message ingestion Enables publishing to Cloudflare Queues from any service via HTTP, removing the previous Workers-only constraint
2 details in Everything
Improved memory efficiency for WebAssembly Workers
May 8, 2025
· release notes
Cloudflare Workers adds FinalizationRegistry via enable_weak_ref compat flag to reduce WASM WASM A binary instruction format for a stack-based virtual machine, maintained by the W3C, that lets code compiled from any language run at near-native speed inside a sandboxed environment across browsers and servers.
Adds enable_weak_ref compatibility flag to opt-in to the new FinalizationRegistry API for WebAssembly WebAssembly A binary instruction format that runs in browsers and server runtimes at near-native speed, letting developers compile C, Rust, or other languages into a portable, sandboxed module any compliant host can execute. Enables automatic freeing of WebAssembly heap allocations via toolchains such as Emscripten and wasm-bindgen, helping resolve Exceeded Memory errors.
2 details in Everything
URL Scanner now supports geo-specific scanning
May 8, 2025
· release notes
Enterprise customers can now specify the geographic region for URL scans to detect location-specific threats via UI or API.
Improved Payload Logging for WAF Managed Rules
May 8, 2025
· release notes
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Payload logs now capture only specific portions of requests that triggered WAF rules instead of entire request segments Matched content is visually highlighted in the WAF UI for faster identification Logs include surrounding context to make diagnostics more effective
3 details in Everything
└──▷ BREAKING ON UPGRADE
! The structure of the encrypted_matched_data field in Logpush has changed from Map<Field, Value> to Map<Field, {Before: bytes, Content: Value, After: bytes}>; existing Logpush processing logic will break unless updated.
Open email links with Browser Isolation
May 8, 2025
· release notes
Cloudflare Email Security adds Open in Browser Isolation icon for email links via Zero Trust settings
Links identified section gains an Open in Browser Isolation icon to open email links in an isolated browser.Adds requirement to enable the setting "Allow users to open a remote browser without the device client" in Zero Trust. Requires assigned Browser Isolation (RBI) seats.
3 details in Everything
Send forensic copies to storage without DLP profiles
May 7, 2025
· release notes
Allow sending DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Enables DLP Forensic Copy jobs to trigger on Allow or Block HTTP policies without a DLP profile attached, increasing flexibility for data handling and forensic investigation.
1 detail in Everything
UDP and ICMP Monitor Support for Private Load Balancing Endpoints
May 6, 2025
· release notes
Cloudflare Load Balancing adds UDP UDP A network protocol that sends individual messages without guaranteeing delivery or order. Applications trade built-in reliability for less overhead and can add their own recovery.
Adds support for ICMP (Layer 3) health monitors to check reachability of private endpoints Adds support for UDP (Layer 4) health monitors for lightweight checks on non-TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it.
2 details in Everything
R2 Dashboard experience gets new updates
May 1, 2025
· release notes
R2 dashboard adds deep links for bucket prefixes, clickable object links, and clearer public access controls
Deep link support for prefix directories enables direct browser navigation within the R2 dashboard without losing state.Objects as clickable links allows users to copy or open object links directly from the list view.Public Development URL rename and clearer status display improve visibility of public access controls.
3 details in Everything
Browser Isolation Overview page for Zero Trust
May 1, 2025
· release notes
New Browser Isolation Overview page in Zero Trust dashboard for centralized management and monitoring
The Zero Trust dashboard now supports dark mode, syncing with core account appearance preferences.
Cloudflare One Appliance supports multiple DNS server IPs
Apr 30, 2025
· release notes
Cloudflare One Appliance supports multiple DNS server IPs in DHCP pool settings.
FQDN Filtering For Gateway Egress Policies
Apr 28, 2025
· release notes
Adds Host, Domain, Content Categories, and Application selectors to Gateway Egress policy builder for FQDN-based egress IP control.
Enables FQDN-based egress IP selection for traffic via WARP client, PAC PAC A Proxy Auto-Configuration file, a JavaScript snippet a browser or OS fetches to decide which proxy server to route each request through, letting cyber tools intercept or redirect traffic without per-app configuration.
1 detail in Everything
Cron triggers are now supported in Python Workers
Apr 24, 2025
· release notes
Python Workers now support scheduled execution via cron triggers.
Adds on_scheduled async handler to Python Workers for executing code on a schedule Adds triggers.crons config key in wrangler.toml to define cron expressions for Python Worker schedules
2 details in Everything
Custom Errors are now Generally Available
Apr 24, 2025
· release notes
Cloudflare Custom Errors GA adds managed rules/assets via dashboard for all paid plans
Custom Error Rules and Custom Error Assets management via the Cloudflare dashboard for all paid plansError Pages renamed from Custom Pages with zone and account configuration supportResponse Header Transform Rules to modify HTTP headers on Custom Errors
3 details in Everything
Metadata filtering and multitenancy support in AutoRAG
Apr 23, 2025
· release notes
AutoRAG adds metadata filtering and multitenancy support via folder and timestamp filters.
Adds filters argument to the search method to specify query scope Supports folder and timestamp as filterable metadata keys
2 details in Everything
Custom fields raw and transformed values support
Apr 18, 2025
· release notes
Cloudflare Logs now support logging both raw and transformed values for request/response headers via per-zone custom field configuration
Custom fields in Logpush jobs now log both raw and transformed values for request and response headers.Default format is raw for request headers and transformed for response headers, which can be overridden.
2 details in Everything
Read multiple keys from Workers KV with bulk reads
Apr 17, 2025
· release notes
Workers KV now supports bulk reads of up to 100 keys in a single API call
Adds bulk reads support to Workers KV via the binding API, allowing retrieval of up to 100 keys in one request
1 detail in Everything
Fixed and documented Workers Routes and Secrets API
Apr 15, 2025
· release notes
Cloudflare Workers Routes API now returns correct pattern and script values; Secrets API docs and SDKs updated
Workers Create Route API (PUT /client/v4/zones/:zone_id/workers/routes) now correctly returns pattern and script fields in the response JSON instead of null/empty strings. Workers and Workers for Platforms Secrets APIs are now publicly documented in Cloudflare OpenAPI OpenAPI A vendor-neutral specification for describing REST APIs in a machine-readable format, maintained by the OpenAPI Initiative. Cyber tools use it to auto-generate clients, documentation, and validation from a single source of truth. cloudflare-typescript (>4.2.0) and cloudflare-python (>4.1.0) SDKs.
2 details in Everything
Workers AI for Developer Week - faster inference, new models, async batch API, expanded LoRA support
Apr 11, 2025
· release notes
Workers AI introduces async batch API, new models (Mistral, Gemma, Qwen), and LoRA LoRA A cheap fine-tuning method that trains small add-on weight matrices instead of the whole model. The result is a few-megabyte adapter that can be swapped in and out of the base model.
Introduces batch API endpoint for asynchronous array-in/async-out inference requests to handle large workloads without capacity errors Adds four new model IDs to the Workers AI catalog: @cf/mistralai/mistral-small-3.1-24b-instruct, @cf/google/gemma-3-12b-it, @cf/qwen/qwq-32b, and @cf/qwen/qwen2.5-coder-32b-instruct Adds new model configuration parameter pooling (accepting cls or mean) for BGE embedding models embedding models Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. Expands LoRA support to 8 specific models and increases max rank limit from 8 to 32, alongside a raised safetensors safetensors A model weight file format that stores only tensors, unlike Python pickle files that can run code when loaded. It is the default on Hugging Face.
4 details in Everything
HTTP redirect and custom block page redirect
Apr 11, 2025
· release notes
Cloudflare Gateway now supports flexible HTTP redirects and custom block page URLs for enhanced policy control.
R2 Data Catalog is a managed Apache Iceberg data catalog built directly into R2 buckets
Apr 10, 2025
· release notes
Cloudflare adds managed Apache Iceberg Apache Iceberg An open table format for large analytic datasets, maintained by the Apache Software Foundation, that gives cyber tools reliable schema evolution, time-travel queries, and atomic commits on object storage or HDFS.
└──▷ TRY IT
Enable Iceberg catalog for a specific R2 bucket via the command line.
copy
$ npx wrangler r2 bucket catalog enable my-bucket
Adds npx wrangler r2 bucket catalog enable <bucket> subcommand to programmatically activate Iceberg catalog support on an R2 bucket Adds R2 Data Catalog toggle in the R2 bucket settings within the Cloudflare dashboard to enable catalog via UI
2 details in Everything
Cloudflare Pipelines now available in beta
Apr 10, 2025
· release notes
Cloudflare introduces Pipelines beta for ingesting high-volume real-time data directly to R2.
└──▷ TRY IT
Provision a new pipeline to ingest clickstream data into an R2 bucket named my-bucket .
copy
$ npx wrangler@latest pipelines create my-clickstream-pipeline --r2-bucket my-bucket Configure a Worker to bind and send data to the newly created pipeline.
text
copy
{
"pipelines": [
{
"pipeline": "my-clickstream-pipeline",
"binding": "PIPELINE"
}
]
}
Adds wrangler pipelines create subcommand to provision new ingestion endpoints. Enables automatic batching and GZIP compression of ingest streams into R2 buckets. Provides a dedicated HTTP ingestion endpoint for each pipeline instance.
3 details in Everything
D1 Read Replication Public Beta enables lower-latency reads via D1 Sessions API and automatic read replicas
Adds env.DB.withSession(bookmark) method to Workers for sequential consistency across queries in a logical session. Adds session.getBookmark() method to retrieve bookmark headers (x-d1-bookmark) for cross-session logical consistency. Introduces automatic, transparently routed read replicas with no additional cost in all supported D1 regions.
3 details in Everything
Cloudflare Snippets are now Generally Available
Apr 9, 2025
· release notes
Cloudflare Snippets generally available on all paid plans with Trace integration.
Snippets are now generally available at no extra cost across all Pro, Business, and Enterprise plans Snippets inherit request modifications from other Cloudflare products and support sequential execution, allowing you to run multiple Snippets on the same request Use Cloudflare Trace to see which Snippets were triggered on a request
3 details in Everything
Hyperdrive now supports custom TLS/SSL certificates
Apr 9, 2025
· release notes
Hyperdrive now supports custom TLS/SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination. wrangler cert commands
└──▷ USE IT
Upload a custom CA certificate bundle to use for verifying Hyperdrive database connections
shell
copy
npx wrangler cert upload certificate-authority --ca-cert your-ca-cert.pem --name your-custom-ca-name
Adds wrangler cert upload certificate-authority and wrangler cert upload mtls-certificate commands to manage CA bundles and client certificate pairs for Hyperdrive Adds --ca-certificate-id, --mtls-certificate-id, and --sslmode options to the wrangler hyperdrive create command
2 details in Everything
Investigate your Workers with the Query Builder in the new Observability dashboard
Apr 9, 2025
· release notes
Cloudflare Workers Observability dashboard GA with Query Builder, logs API, and wrangler.toml config keys
Adds the Invocations view in the Workers Observability dashboard to group logs by specific trigger events. Adds the Events view to display logs ordered by timestamp across all Workers. Adds an Investigate tab with a UI Query Builder for filtering, grouping, and visualizing Workers Logs. Makes Workers Logs generally available with ingestion and storage for up to 7 days.
4 details in Everything
Cloudflare Zero Trust SCIM User and Group Provisioning Logs
Apr 9, 2025
· release notes
Cloudflare Zero Trust adds SCIM SCIM A standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave. IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems.
New Logs -> SCIM provisioning section in the Zero Trust Dashboard for auditing SCIM create, update and delete events from any enabled IdP.
1 detail in Everything
Cloudflare Secrets Store now available in Beta
Apr 9, 2025
· release notes
Cloudflare Secrets Store enters Beta, enabling centralized account-level secret management via UI and Wrangler CLI
Adds the wrangler secrets-store store create <name> --remote command to provision a Secrets Store from the CLI Unveils the Secrets Store tab in the Cloudflare dashboard for creating stores and managing secrets (create, duplicate, update, scope, delete) Extends Workers UI to bind account-level Secrets Store entries to Workers directly
3 details in Everything
CPU time and Wall time now published for Workers Invocations
Apr 9, 2025
· release notes
CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware.
Adds cpu_time and wall_time fields to the Invocation Log in Workers Logs Adds cpu_time and wall_time fields to the top level of the Workers Trace Events object for Tail Workers Adds cpu_time and wall_time fields to the top level of the Workers Trace Events object for Workers Logpush
3 details in Everything
Hyperdrive introduces support for MySQL and MySQL-compatible databases
Apr 8, 2025
· release notes
Cloudflare Hyperdrive now supports MySQL and MySQL-compatible databases including RDS, Aurora, Cloud SQL, Azure DB, PlanetScale and MariaDB.
The Cloudflare Vite plugin is now Generally Available
Apr 8, 2025
· release notes
Cloudflare's @cloudflare/vite-plugin reaches GA v1.0, enabling Workers runtime in Vite dev and builds.
The @cloudflare/vite-plugin (v1.0) is generally available, allowing Vite development to run code in the workerd Workers runtime. Framework support for React Router v7 (Remix) is added, providing full support for the Cloudflare developer platform without additional build steps.
2 details in Everything
Deploy a Workers application in seconds with one-click
Apr 8, 2025
· release notes
Adds one-click Deploy to Cloudflare button via URL to auto-provision resources and configure CI/CD for Workers apps.
https://deploy.workers.cloudflare.com/button provides a Markdown link that initiates the deployment workflow when clicked.Supports url=<YOUR_GIT_REPO_URL> query parameter to specify the source repository for automatic cloning and setup. Automatically provisions Workers KV, D1, or R2 resources bound to the Worker upon deployment from the button flow. Configures Workers Builds CI/CD automatically for pushes to the production branch of the newly created repository. Generates and posts preview URLs as GitHub comments on pull requests for non-production branches.
5 details in Everything
Local development support for Email Workers
Apr 8, 2025
· release notes
Wrangler adds local development support for Email Workers with a new /cdn-cgi/local/email endpoint
Email Workers can now be tested locally for receiving, replying, and sending emails using wrangler dev
1 detail in Everything
Improved support for Node.js Crypto and TLS APIs in Workers
Apr 8, 2025
· release notes
Cloudflare Workers now exposes node:crypto and node:tls APIs when nodejs_compat is enabled.
node:crypto module is now available in Workers with nodejs_compat for signing, verifying, encrypting, and decrypting datanode:tls module is now available in Workers with nodejs_compat, providing connect, TLSSocket , checkServerIdentity, and createSecureContext
2 details in Everything
Build MCP servers with the Agents SDK
Apr 7, 2025
· release notes
Cloudflare Agents SDK now supports building remote MCP MCP Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. McpAgent class and exports agent context.
Introduces McpAgent class to build remote MCP (Model Context Protocol Model Context Protocol Model Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. Adds context export from agents package to access current agent, request, and WebSocket WebSocket A protocol that upgrades an HTTP connection into a persistent, full-duplex channel, letting a server push data to a client without repeated polling. Cyber tools use it for real-time event streaming and live command output.
2 details in Everything
Durable Objects on the Workers Free plan, enabling stateful serverless apps and AI agents at zero cost.
Adds Durable Object support to the Workers Free plan for building stateful serverless applications and AI agents.
1 detail in Everything
Create fully-managed RAG pipelines for your AI applications with AutoRAG
Apr 7, 2025
· release notes
AutoRAG open beta allows fully-managed RAG RAG Retrieval-augmented generation: looking up relevant documents and adding them to the prompt before the model answers. It grounds responses in private or current data without retraining.
Adds AutoRAG service for fully-managed retrieval-augmented generation retrieval-augmented generation Retrieval-augmented generation: looking up relevant documents and adding them to the prompt before the model answers. It grounds responses in private or current data without retraining. Supports custom Workers AI models, chunking strategies, and system prompts in the pipeline Enables continuous index synchronization with data sources like R2 buckets Provides querying via API and Workers binding endpoints
4 details in Everything
Browser Rendering REST API is Generally Available, with new endpoints and a free tier
Apr 7, 2025
· release notes
Cloudflare Browser Rendering REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
/json endpoint to extract structured data from webpages/links endpoint to retrieve all links from a webpage/markdown endpoint to convert webpage content into Markdown formatBrowser Rendering REST API Generally Available for use outside of Workers applications Browser Rendering available on the Cloudflare Workers Free plan
5 details in Everything
SQLite in Durable Objects GA with 10GB storage per object
Apr 7, 2025
· release notes
SQLite in Durable Objects GA with 10GB storage per object
Adds SQL and point-in-time recovery methods to the Storage API for SQLite-backed Durable Objects, enabling relational data modeling and SQL querying. Introduces new_sqlite_classes Wrangler configuration option to designate Durable Object classes as SQLite-backed.
2 details in Everything
Capture up to 256 KB of log events in each Workers Invocation
Apr 7, 2025
· release notes
Increases Workers log event capture limit to 256 KB per invocation (doubled from 128 KB).
Captures up to 256 KB of log events in each Worker invocation
1 detail in Everything
Cloudflare Workflows GA introduces step.waitForEvent, increased concurrency limits, and vitest support.
Adds step.waitForEvent API to enable human-in-the-loop human-in-the-loop Human in the loop, involving a person in an otherwise automated workflow. The person can review, approve, correct or supply information before work continues. Increases concurrent Workflow instance limit to 4,500. Adds vitest support for testing Workflows locally and in CI/CD pipelines. Adds new CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware. Supports increased CPU limits for Workers (up to 5 minutes of CPU time per instance).
5 details in Everything
Workers Fetch API can override Cache Rules
Apr 4, 2025
· release notes
Workers fetch() now accepts a cf object to programmatically override Cache Rules like cacheTtl and cacheEverything.
Pass cf object as second argument to fetch() to override default Cache Rules. New cf.cacheTtl option for custom TTL TTL Time to live, a limit on how long data remains valid or how far a packet can travel. Caches use a time limit; IP packets use a hop limit. New cf.cacheTtlByStatus option to set TTLs based on response status codes. New cf.cacheEverything option to cache all content types beyond defaults. New cf.cacheKey option for custom cache keys (Enterprise only).
+1 more
show less
New cf.cacheTags option to append tags for targeted cache purging.
6 details in Everything
All cache purge methods now available for all plans
Apr 3, 2025
· release notes
All plans now support every Cloudflare cache purge method previously reserved for Enterprise.
Purge Everything clears all cached content associated with a website for all plans Purge by Prefix targets URLs sharing a common prefix for all plans Purge by Hostname invalidates content by specific hostnames for all plans Purge by URL (single-file purge) precisely targets individual URLs for all plans Purge by Tag uses Cache-Tag response headers to invalidate grouped assets for all plans
5 details in Everything
Adds two free CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic. SaaS SaaS Software delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally.
Enables SaaS integration for directory user sync and delivered email actions Enables separate SaaS integration for discovering CASB findings from another provider
2 details in Everything
Register and renew .ai and .shop domains at cost
Mar 27, 2025
· release notes
Cloudflare Registrar adds .ai and .shop domain support at cost with native DNS/CDN CDN A content delivery network, servers distributed across locations that cache and serve content near readers. It can reduce loading time and traffic to the original server. SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination.
Register and renew .ai and .shop domains at cost without markups
1 detail in Everything
Audit logs (version 2) - Beta Release
Mar 27, 2025
· release notes
Cloudflare introduces beta v2 Audit Logs API with automated, standardized logging and expanded coverage.
Automates audit log generation via API Shield based on OpenAPI OpenAPI A vendor-neutral specification for describing REST APIs in a machine-readable format, maintained by the OpenAPI Initiative. Cyber tools use it to auto-generate clients, documentation, and validation from a single source of truth. Expands audit log coverage from 75% to 95%, including /accounts, /zones, and /organizations endpoints.
2 details in Everything
Updates to Account Home - Quick actions, traffic insights, Workers projects, and more
Mar 26, 2025
· release notes
Account Home gains recent Workers projects tab, traffic insights, quick actions menu, and starred domain persistence.
Adds a Developer Platform tab on Account Home to surface recently-modified Workers projects Adds traffic and security insights dashboard showing key metrics and trends for domains Adds quick actions (1-2 clicks) for account, domain, and Workers operations via the 3-dot menu Improves starred domain filtering to persist user preference across sessions
4 details in Everything
Run Workers for up to 5 minutes of CPU-time
Mar 26, 2025
· release notes
Workers now supports cpu_ms config to run for up to 5 minutes of CPU CPU The main general-purpose processor in a computer. It runs application instructions and coordinates work with memory and other hardware.
Adds cpu_ms configuration key in Wrangler config to set Worker CPU time limits up to 300,000ms (5 minutes).
1 detail in Everything
Cloudflare Workers source maps are GA with gzipped size limit and config support in Wrangler.
Source maps for Workers are Generally Available, supporting uploads up to 15 MB gzipped (up from 15 MB uncompressed) Adds upload_source_maps configuration key to enable source map upload in Pages Function or Worker Wrangler config files
2 details in Everything
AI Gateway launches Realtime WebSockets API
Mar 21, 2025
· release notes
AI Gateway adds Realtime WebSockets API for persistent low-latency AI connections with OpenAI, Gemini Live, Cartesia, and ElevenLabs.
Adds the Realtime WebSockets API endpoint at wss://gateway.ai.cloudflare.com/v1/<account_id>/<gateway>/openai to enable persistent, low-latency AI interactions. Enables real-time text and speech interactions with models from OpenAI Realtime API, Google Gemini Live API, Cartesia, and ElevenLabs through a single integration surface.
2 details in Everything
Secure DNS Locations Management User Role
Mar 21, 2025
· release notes
Cloudflare adds Secure DNS Locations Management User Role for granular PDNS endpoint access
Introduces the Secure DNS Locations Management User Role (Cloudflare Zero Trust) to allow external partners to administer DNS location endpoints without overprovisioning permissions
1 detail in Everything
Workers AI adds toMarkdown utility method and associated REST endpoint for converting documents to Markdown.
Adds the env.AI.toMarkdown() binding in Workers AI runtime for programmatic document conversion Exposes a new REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
2 details in Everything
Cloudflare Agents SDK adds CORS CORS A browser mechanism that lets a server declare which foreign origins may read its HTTP responses, enforced by the browser to block unauthorized cross-site requests from JavaScript. unstable_callable() , and a scheduling module
Supports cors: true in routeAgentRequest to enable permissive CORS headers for Agent responses Adds @unstable_callable() decorator for defining RPC RPC Remote Procedure Call, a protocol that lets a program execute a function on another machine as if it were local, giving cyber tools a structured way to communicate across processes or hosts without managing raw sockets. Introduces experimental /schedule module with prompt/schema for adding scheduling to your app
3 details in Everything
New API Posture Management for API Shield
Mar 18, 2025
· release notes
New automatic risk labeling for API endpoints in Cloudflare API Shield.
Adds cf-risk-sensitive label for sensitive data detected by WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server. Adds cf-risk-missing-auth label when configured session ID is absent from requests Adds cf-risk-mixed-auth label when some requests have session ID and others do not Adds cf-risk-missing-schema label for endpoints with no active schema despite learned schema availability Adds cf-risk-error-anomaly label for recent increases in response errors over 24 hours
+3 more
show less
Adds cf-risk-latency-anomaly label for recent increases in response latency over 24 hours Adds cf-risk-size-anomaly label for spikes in response body size over 24 hours Adds beta labels cf-risk-bola-enumeration and cf-risk-bola-pollution for suspected BOLA BOLA Broken Object Level Authorization, an API vulnerability class where a server fails to verify that the requesting user owns or may access the object ID they supply, letting attackers read or modify other users' data.
8 details in Everything
Leaked Credentials Insights in Cloudflare Radar
Mar 18, 2025
· release notes
Cloudflare Radar adds leaked credentials detection endpoints for aggregate HTTP auth request trends
Adds GET /leaked_credential_checks/summary/{dimension} to retrieve summaries of HTTP authentication requests distribution across two dimensions. Adds GET /leaked_credential_checks/timeseries_groups/{dimension} to retrieve timeseries data for HTTP authentication requests distribution across two dimensions.
2 details in Everything
Workers AI adds BGE-M3 embeddings embeddings Lists of numbers a model produces to represent the meaning of text, images or code, so similar items sit close together. They power semantic search and RAG. reranker reranker A model that re-scores a first batch of search results against the query and reorders them, more accurately than the fast first-stage search.
Adds @cf/baai/bge-m3 multi-lingual embeddings model supporting dense, multi-vector, and sparse retrieval for over 100 languages Adds @cf/baai/bge-reranker-base, the first reranker model outputting similarity scores for RAG RAG Retrieval-augmented generation: looking up relevant documents and adding them to the prompt before the model answers. It grounds responses in private or current data without retraining. Graduates @cf/openai/whisper-large-v3-turbo speech-to-text model from beta to general availability with new pricing Adds @cf/myshell-ai/melotts, a text-to-speech model generating MP3 audio from text input
4 details in Everything
Cloudflare One Agent for iOS (version 1.10)
Mar 17, 2025
· release notes
Cloudflare One Agent for iOS v1.10 adds team name insertion by URL during enrollment
Retry Pages & Workers Builds Directly from GitHub
Mar 17, 2025
· release notes
Cloudflare Pages and Workers builds can now be retried directly from GitHub via the failed Check Run.
Import `env` to access bindings in your Worker's global scope
Mar 17, 2025
· release notes
Cloudflare Workers now allows importing env to access bindings in global scope
Adds importable env from cloudflare:workers to access secrets and environment variables at the top-level of a Worker
1 detail in Everything
Cloudflare One Agent for Android (version 2.4)
Mar 17, 2025
· release notes
Cloudflare One Agent 2.4 GA is now available on Android, enabling team-specific enrollment workflows and improved error messaging for mobile clients.
Adds team name insertion by URL to the enrollment flow for Cloudflare One Agent on Android
1 detail in Everything
Set breakpoints and debug your Workers tests with @cloudflare/vitest-pool-workers
Mar 13, 2025
· release notes
Dev tooling update for debugging Workers tests.
└──▷ TRY IT
Run Workers tests in debug mode to attach VS Code or Chrome DevTools breakpoints.
copy
$ vitest --inspect --no-file-parallelism
Magic Firewall now supports the new managed Cloudflare IP Ranges list for source/destination address policies.
Adds Cloudflare IP Ranges to the dropdown menu for Magic Firewall policy conditions (is in list / is not in list)
1 detail in Everything
Threaded replies now possible in Email Workers
Mar 12, 2025
· release notes
Cloudflare Email Workers now support threaded replies with DMARC validation and loop protection
Enables message.reply() in Email Workers to send threaded responses when the incoming email has valid DMARC and matches sender/recipient domains. Adds a limit of 100 entries in the References list to prevent abuse or accidental loops in email threading. Requires replies to be sent within the same EmailMessage event to maintain thread continuity.
3 details in Everything
Access your Worker's environment variables from process.env
Mar 11, 2025
· release notes
Adds nodejs_compat_populate_process_env flag to populate Worker process.env with secrets and variables
└──▷ BREAKING ON UPGRADE
! After April 1, 2025, populating process.env will become the default behavior when both nodejs_compat is enabled and compatibility_date is after 2025-04-01 .
Cloudflare One Agent now supports Endpoint Monitoring
Mar 7, 2025
· release notes
Cloudflare One Agent v2025.1.861 adds Endpoint Monitoring for device health metrics
Hyperdrive reduces query latency by up to 90% and now supports IP access control lists
Mar 7, 2025
· release notes
Hyperdrive connection pooling and IP access control list access control list An access control list, a set of rules allowing or denying operations for particular users, services or network addresses. It decides who can use a resource.
Hyperdrive pools database connections in regions near the database, reducing uncached query latency by up to 90% Hyperdrive now connects using Cloudflare's standard IP address ranges, enabling IP access control list configuration for database firewalls
2 details in Everything
One-click Logpush Setup with R2 Object Storage
Mar 6, 2025
· release notes
One-click Logpush setup with R2 bucket creation integrated into the workflow
Introducing Media Transformations from Cloudflare Stream
Mar 6, 2025
· release notes
Cloudflare adds cdn-cgi/media URL path for dynamic video transformations
└──▷ TRY IT
Dynamically resize a video to 640px width and output an optimized MP4 via the new URL pattern.
copy
$ https://example.com/cdn-cgi/media/width=640/<SOURCE-VIDEO>
Adds the /cdn-cgi/media/<OPTIONS>/<SOURCE-VIDEO> URL pattern to transform short-form video and image files directly via HTTP requests. Enables on-the-fly optimization of source assets (e.g., width adjustment) into optimized MP4 outputs without requiring asset migration or additional storage.
2 details in Everything
Set retention polices for your R2 bucket with bucket locks
Mar 6, 2025
· release notes
Cloudflare adds wrangler r2 bucket lock add to set retention policies on R2 buckets via bucket locks.
Adds the wrangler r2 bucket lock add subcommand to configure bucket locks for R2 objects. Supports locking objects indefinitely using the --retention-indefinite flag in Wrangler.
2 details in Everything
Gain visibility into user actions in Zero Trust Browser Isolation sessions
Mar 4, 2025
· release notes
New Logpush integration for Browser Isolation tracks copy/paste, downloads/uploads, and printing actions.
Enables Logpush jobs to receive new browser isolation event types including copy, download, upload, and print within Remote Browser Isolation sessions.
1 detail in Everything
New SAML and OIDC Fields and SAML transforms for Access for SaaS
Mar 3, 2025
· release notes
New SAML SAML A standard for passing signed identity assertions between a sign-in provider and an application. It lets a user sign in through their organization's identity provider. OIDC OIDC OpenID Connect, a sign-in protocol built on OAuth 2.0. An application uses identity information from a trusted provider instead of maintaining a separate password for each user. JSONata JSONata A query and transformation language for JSON data, maintained as an open-source project. Cyber tools use it to extract, reshape, and map JSON payloads without writing custom parsing code. SaaS SaaS Software delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally.
Adds OIDC Group Filtering via RegEx to control application access based on group membership Adds OIDC Claim mapping from an IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. Adds OIDC token lifetime control to set the duration of OIDC tokens for Access applications Adds Advanced OIDC auth flows (hybrid and implicit) support for broader SaaS integration coverage Adds improved SAML attribute mapping from an IdP for more flexible identity configuration
+1 more
show less
Adds JSONata expressions for SAML transformations to fully customize SAML identity statements sent to apps
6 details in Everything
Use Logpush for Email security detections
Mar 1, 2025
· release notes
Cloudflare adds Logpush support for Email security detection logs in Enterprise packages
Use the latest JavaScript features with Wrangler CLI v4.0.0-rc.0
Prerelease
Feb 28, 2025
· release notes
Wrangler v4 RC adds modern JS features and local-datastore defaults
Adds support for the using keyword from Explicit Resource Management Adds support for Import attributes (e.g., import data from "./data.json" with { type: "json" })
2 details in Everything
└──▷ BREAKING ON UPGRADE
! Deprecated features removed: legacy_assets config property, node_compat config property, wrangler version subcommand (use wrangler --version), and getBindingsProxy() (use getPlatformProxy() ) no longer work! Minimum Node.js version is now 18 or later
Cloudflare Radar introduces DNS Insights API endpoints for query distribution across 10 dimensions.
Adds the /dns/timeseries endpoint to retrieve aggregated DNS query volume over time Adds the /dns/summary/{dimension} endpoint to retrieve summaries of DNS query distribution across ten dimensions Adds the /dns/timeseries_groups/{dimension} endpoint to retrieve timeseries data for DNS query distribution across ten dimensions
3 details in Everything
Cloudflare Browser Rendering REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Adds POST /client/v4/accounts/<accountId>/browser-rendering/screenshot endpoint to capture web page screenshots Adds POST /client/v4/accounts/<accountId>/browser-rendering/pdf endpoint to convert web pages into PDFs Adds POST /client/v4/accounts/<accountId>/browser-rendering/content endpoint to retrieve full HTML from a page Adds POST /client/v4/accounts/<accountId>/browser-rendering/snapshot endpoint to capture HTML and screenshot in one request Adds POST /client/v4/accounts/<accountId>/browser-rendering/scrape endpoint to extract specific elements from a page
5 details in Everything
Check status of Email security or Area 1
Feb 27, 2025
· release notes
Adds monitoring of Email security and Area 1 operational status on the Cloudflare Status page
Introducing Guardrails in AI Gateway
Feb 26, 2025
· release notes
AI Gateway adds Guardrails for monitoring and blocking harmful content in prompts and responses
Adds Guardrails configuration in AI Gateway settings to enable or disable content moderation Adds Evaluation scope setting to select moderation targets: user prompts, model responses, or both Adds Hazard categories configuration to specify monitored categories and define actions (block or flag) for detected content
3 details in Everything
Workers AI now supports structured JSON outputs.
Feb 25, 2025
· release notes
Workers AI adds JSON mode JSON mode Forcing a model's response to match a given format or JSON schema, so software can parse it reliably instead of hoping the text is well formed. structured output structured output Forcing a model's response to match a given format or JSON schema, so software can parse it reliably instead of hoping the text is well formed. response_format API parameter.
Enables typed extraction of data from AI models without manual parsing, using OpenAI SDK compatibility
1 detail in Everything
Cloudflare adds DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Adds DLP Assist integration with Microsoft 365 to allow deploying an Email DLP solution for free. Enables configuring DLP policies in Cloudflare to trigger behaviors like banners, pre-send alerts, or delivery prevention in Outlook. Expands availability of this feature to Enterprise and Enterprise + PhishGuard email security packages.
3 details in Everything
Cloudflare introduces the Agents SDK for building and deploying AI Agents on Workers.
Adds the agents npm package to enable building AI Agents with tool calling tool calling A model's ability to answer with a structured request to run a named function or API, which the application executes and returns. It is how agents take actions.
1 detail in Everything
Concurrent Workflow instances limits increased.
Feb 25, 2025
· release notes
Cloudflare Workflows concurrent instance limit raised from 100 to 4,500 for Paid plan users.
Increases the maximum number of concurrent (running) Workflow instances from 100 to 4,500 for all Workers Paid plan users.
1 detail in Everything
Cloudflare introduces the Images binding for Workers, enabling direct image transformation and output.
Adds the images binding to Workers, allowing code-level interaction with Cloudflare Images API without requiring URL access.
1 detail in Everything
Super Slurper now supports migrations from all S3-compatible storage providers
Feb 24, 2025
· release notes
Super Slurper now supports migrations from all S3-compatible S3-compatible An object-storage API that mirrors Amazon S3's HTTP interface, so any client or cyber tool written for AWS S3 works unchanged against any compliant storage backend.
Enables Super Slurper to migrate data from any S3-compatible object storage provider to Cloudflare R2 Adds support for migration sources such as MinIO, Wasabi, Backblaze B2, and DigitalOcean Spaces
2 details in Everything
Workers for Platforms - Instant dispatch for newly created User Workers
Feb 20, 2025
· release notes
Workers for Platforms User Workers now deploy synchronously on first upload
First-time uploads of User Workers are now deployed synchronously
1 detail in Everything
Autofix Worker name configuration errors at build time
Feb 20, 2025
· release notes
Workers Builds automatically detect and fix configuration errors via pull request before build.
Adds automatic detection of Worker name mismatches between wrangler.toml or wrangler.jsonc and the Cloudflare dashboard during Builds.
1 detail in Everything
Rewind, Replay, Resume: Introducing DVR for Stream Live
Feb 14, 2025
· release notes
Cloudflare Stream Live adds DVR playback via dvrEnabled=true query parameter.
Adds dvrEnabled=true query parameter to player embed and manifest URLs to enable on-demand seeking in live streams Enables viewers to pause, rewind, and seek through active live broadcasts instead of being locked to the live edge
2 details in Everything
Customize queue message retention periods
Feb 14, 2025
· release notes
Cloudflare Queues adds configurable message retention periods (60s-14 days) via Wrangler CLI and UI.
└──▷ USE IT
Set a queue to expire messages after exactly 10 minutes to reduce storage costs for high-volume ephemeral data.
shell
copy
wrangler queues update my-queue --message-retention-period-secs 600
Adds wrangler queues update <name> --message-retention-period-secs <seconds> to set queue retention from 60 seconds to 14 days
1 detail in Everything
Build AI Agents with Example Prompts
Feb 14, 2025
· release notes
Cloudflare adds an example prompt for building AI agents on Workers with Workflows
Introduces the <user_prompt> tag format for pasting custom instructions into supported AI models like Claude 3.5 Sonnet and OpenAI's o3-mini.
1 detail in Everything
Upload a certificate bundle with an RSA and ECDSA certificate per custom hostname
Feb 14, 2025
· release notes
Adds per-custom-hostname certificate bundling via the API
Adds custom_cert_bundle array and bundle_method: "force" support in the POST /zones/$ZONE_ID/custom_hostnames API to upload RSA RSA The oldest widely used public-key algorithm, for both encryption and signatures, with security resting on factoring large numbers. A large quantum computer would break it. ECDSA ECDSA The elliptic-curve signature algorithm behind most TLS certificates, blockchains and many hardware keys. It is one of the algorithms post-quantum signatures are meant to replace.
1 detail in Everything
Configurable multiplexing HTTP/2 to Origin
Feb 12, 2025
· release notes
Enterprise plans can now configure HTTP/2 multiplexing settings for origin connections via Dashboard or API.
Adds configurable HTTP/2 multiplexing settings for Enterprise-origin connections to control concurrent streams and optimize connection reuse
1 detail in Everything
Cloudflare increases limits for Bulk Redirects, Connectors, Custom Errors, Snippets, and Rules across all plans
Increases Cloudflare Bulk Redirects limit to 10,000 (Free), 25,000 (Pro), 50,000 (Business), or 1,000,000 (Enterprise) Increases Cloud Connector limit to 10 (Free) or 300 (Enterprise) Increases Custom Errors limit to 25 (Pro), 50 (Business), or 300 (Enterprise) Increases Snippets limit to 25 (Pro), 50 (Business), or 300 (Enterprise) Increases Cache Rules, Configuration Rules, Compression Rules, Origin Rules, Single Redirects, and Transform Rules limits to 300 for Enterprise accounts
5 details in Everything
Custom Errors (beta): Stored Assets & Account-level Rules
Feb 11, 2025
· release notes
New beta feature allowing external error page asset storage and account-level rule definition via API.
└──▷ TRY IT
Upload a maintenance page hosted on an external server to Cloudflare's edge for use in custom errors.
copy
$ curl "https://api.cloudflare.com/client/v4/zones/{zone_id}/custom_pages/assets" \
--header "Authorization: Bearer <API_TOKEN>" \
--header 'Content-Type: application/json' \
--data '{
"name": "maintenance",
"description": "Maintenance template page",
"url": "https://example.com/"
}' Reference a stored asset in a Custom Error rule to serve the uploaded maintenance page for specific URIs.
copy
$ curl --request PUT \
"https://api.cloudflare.com/client/v4/zones/{zone_id}/rulesets/phases/http_custom_errors/entrypoint" \
--header "Authorization: Bearer <API_TOKEN>" \
--header 'Content-Type: application/json' \
--data '{
"rules": [
{
"action": "serve_error",
"action_parameters": {
"asset_name": "maintenance",
"content_type": "text/html",
"status_code": 503
},
"enabled": true,
"expression": "http.request.uri.path contains \"error\""
}
]
}'
Create and deploy Workers from Git repositories
Feb 7, 2025
· release notes
New Workers dashboard workflow to create and auto-deploy from Git repos or templates
Adds the ability to import an existing GitHub/GitLab repository directly into the Workers dashboard to enable automatic builds on branch pushes. Adds a new selection of production-ready template examples (e.g., Astro, Remix, Next) that provision required resources like D1 or Workers AI upon deployment.
2 details in Everything
Request timeouts and retries with AI Gateway
Feb 6, 2025
· release notes
AI Gateway adds configurable request timeouts and retries via new headers for improved reliability
Adds cf-aig-request-timeout header to set request timeout thresholds directly to a provider. Adds cf-aig-max-attempts, cf-aig-retry-delay, and cf-aig-backoff headers to enable automatic request retries with constant, linear, or exponential backoff strategies.
2 details in Everything
Cloudflare CSAM Scanning Tool now onboards with a verified email instead of external reporting credentials.
Replaces the previous requirement for external reporting credentials with a simple verified email address to enable the CSAM Scanning Tool. The tool hashes images as they enter the Cloudflare cache and checks them against a database of known abusive images, automatically blocking matched content URLs.
2 details in Everything
Expanded AI insights in Cloudflare Radar
Feb 4, 2025
· release notes
Cloudflare Radar adds daily service rankings, weekly robots.txt AI bot analysis, and Workers AI inference data via new API endpoints.
Adds daily Internet services ranking insights via /ranking/internet_services/top and /ranking/internet_services/timeseries_groups API endpoints Adds weekly AI-focused robots.txt analysis via /robots_txt/top/user_agents/directive and /robots_txt/top/domain_categories API endpoints Adds Workers AI inference model tracking via /ai/inference/summary/{dimension} and /ai/inference/timeseries_groups/{dimension} API endpoints
3 details in Everything
Block files that are password-protected, compressed, or otherwise unscannable.
Feb 3, 2025
· release notes
Cloudflare DLP DLP Data Loss Prevention: a category of controls that inspect and block sensitive data from leaving an organisation via email, web, or removable media, giving cyber tools a policy enforcement layer over data in motion and at rest.
Download and Upload File Types traffic selectors in HTTP policies can now match Password-protected Microsoft Office document , Password-protected PDF , Password-protected ZIP archive , and Unscannable ZIP archive for blocking.Gateway HTTP policies automatically block these unscannable file types when the corresponding traffic selector is applied, extending existing DLP capabilities to previously bypassed content.
2 details in Everything
Workers Metrics dashboard revamped with drag-and-select timepicker, histograms for cumulative metrics, and version-specific deployment monitoring.
Adds a graphical timepicker for drag-and-select metric selection in the Workers Metrics dashboard Introduces histogram visualization for cumulative metrics to bucket and compare rates over time Enables direct interaction with version numbers in the legend to focus on specific Worker versions Provides monitoring and comparison capabilities for active gradual deployments within the new interface
4 details in Everything
Workers for Platforms now supports Static Assets
Jan 31, 2025
· release notes
Workers for Platforms adds static asset hosting via env.ASSETS.fetch()
Allows attaching static assets (HTML, CSS, JavaScript, images) directly to User Workers via the Workers for Platforms API or Wrangler
1 detail in Everything
Expanded language support for Stream AI Generated Captions
Jan 30, 2025
· release notes
Stream AI captions now support Czech, Dutch, French, German, Italian, Japanese, Korean, Polish, Portuguese, Russian, and Spanish.
Adds CS, NL, FR, DE, IT, JA, KO, PL, PT, RU, ES language support to Stream AI Generated Captions.
1 detail in Everything
AI Gateway Introduces New Worker Binding Methods
Jan 30, 2025
· release notes
Cloudflare AI Gateway adds new Worker binding methods (patchLog, getLog, run) for direct integration
Adds patchLog to the Workers bindings API for sending feedback and updating metadata Adds getLog to the Workers bindings API for retrieving detailed log information Adds run to the Workers bindings API for executing universal requests to any AI Gateway provider
3 details in Everything
Cloudflare introduces a new single-page Snippets code editor for editing code and rules together
Enables single-page editing of Snippet code and its associated rule in the Cloudflare dashboard.
1 detail in Everything
Automatic configuration for private databases on Hyperdrive
Jan 28, 2025
· release notes
Hyperdrive now auto-configures Cloudflare Access, Service Token, and Policies for private database connections.
Support for Node.js DNS, Net, and Timer APIs in Workers
Jan 28, 2025
· release notes
Workers now supports Node.js DNS, Net, and Timer APIs when nodejs_compat flag is enabled
Adds node:net API support (including net.Socket, net.BlockList, net.SocketAddress) for TCP TCP A network protocol that delivers a reliable, ordered stream of bytes between two endpoints. It detects lost data and retransmits it. nodejs_compat compatibility flag. Adds node:dns API support for DNS resolution via Cloudflare DNS at 1.1.1.1 in Workers with nodejs_compat compatibility flag. Adds node:timers API support (setTimeout, setInterval, setImmediate) for scheduling functions in Workers with nodejs_compat compatibility flag.
3 details in Everything
Workers KV namespace limits increased to 1000
Jan 28, 2025
· release notes
Workers KV namespace limit raised from 200 to 1000 per account for all plans.
Increases the maximum number of Workers KV namespaces allowed per Cloudflare account from 200 to 1000.
1 detail in Everything
WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Cloudflare Managed Ruleset rule 100303 (Command Injection - Nslookup) now blocks requests that were previously only logged. Cloudflare Managed Ruleset rule 100534 (Web Shell Activity) now blocks requests that were previously only logged.
2 details in Everything
Export SSH command logs with Access for Infrastructure using Logpush
Jan 15, 2025
· release notes
This release introduces new telemetry capabilities by enabling SSH command log export for Access for Infrastructure through the existing Logpush integration.
Adds the ability to send SSH command logs from Access for Infrastructure to Logpush destinations
1 detail in Everything
Increased Workflows limits and improved instance queueing.
Jan 15, 2025
· release notes
Cloudflare Workflows now supports 1024 steps, instanceId in WorkflowEvent, and queue handling via pause/resume.
Increases the maximum number of steps per Workflow to 1024. sleep steps are excluded from this limit. Adds instanceId property to the WorkflowEvent type, allowing retrieval of the current instance ID from within a running workflow instance. Adds support for pause and resume actions for Workflow instances currently in a queued state.
3 details in Everything
Cloudflare introduces Rules Overview interface to manage and debug all rules in one place
Adds the Rules > Overview UI screen for managing all Cloudflare Rules in a single page
1 detail in Everything
Smart Tiered Cache optimizes Load Balancing Pools
Jan 8, 2025
· release notes
Smart Tiered Cache now automatically selects the optimal Upper Tier data center for all origins in a Load Balancing Pool to improve cache hit rates and reduce origin load.
AI Gateway adds DeepSeek as a Provider
Jan 2, 2025
· release notes
AI Gateway adds DeepSeek as a supported provider
Faster Workers Builds with Build Caching and Watch Paths
Dec 29, 2024
· release notes
Workers Builds now supports project-wide build caching and configurable watch paths.
Adds project-wide Build Caching to cache dependencies and outputs between builds in Workers Builds.
1 detail in Everything
Increased transparency for phishing email submissions
Dec 19, 2024
· release notes
Adds a Reclassification tab in Zero Trust dashboard to view phishing submission outcomes
New Escalate user submissions capability in Cloudflare Email security for reclassification by the team.
Adds Escalate action in User submissions view to create a team request for reclassification of machine-reviewed submissions. Enables escalation of user submissions from submission alias, PhishNet, and API sources to Cloudflare team for human review.
2 details in Everything
Establish BGP peering over Direct CNI circuits
Dec 17, 2024
· release notes
Add MD5-authenticated eBGP peering over Direct CNI circuits for Magic WAN and Transit via dashboard
Adds MD5 authentication support for eBGP sessions established between customer devices and the Magic routing table when connected via a Direct Cloudflare Network Interconnect (CNI) on-ramp. Enables dynamic route exchange by establishing an eBGP session between local network devices and the Magic WAN / Magic Transit service over Direct CNI circuits.
2 details in Everything
Adds cloudflare_snippet and cloudflare_snippet_rules Terraform resources to manage Snippets via IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup.
Adds the cloudflare_snippet Terraform resource to deploy and update Snippet code as infrastructure-as-code Adds the cloudflare_snippet_rules Terraform resource to define rules that trigger Snippets based on expressions
2 details in Everything
Generate customized terraform files for building cloud network on-ramps
Dec 5, 2024
· release notes
Magic Cloud now scans and discovers existing network resources to generate customized Terraform files for Magic WAN on-ramps.
Cloud Connector now supports routing traffic to R2 buckets via cloudflare_r2 provider
Find security misconfigurations in your AWS cloud environment
Nov 22, 2024
· release notes
Cloudflare CASB CASB A Cloud Access Security Broker is a policy-enforcement proxy, on-premises or cloud-hosted, that sits between users and cloud services to provide visibility, compliance controls, and threat protection over SaaS and IaaS traffic.
Adds Cloud & SaaS SaaS Software delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally.
1 detail in Everything
Smart Tiered Cache automatically optimizes R2 caching
Nov 20, 2024
· release notes
Cloudflare introduces Smart Tiered Cache to automatically optimize R2 egress costs and latency
Reduces R2 egress charges by routing cache misses through a proxied Upper Tier before reaching the origin bucket
1 detail in Everything
Bypass caching for subrequests made from Cloudflare Workers, with Request.cache
Nov 11, 2024
· release notes
Adds Request.cache with no-store to bypass caching for subrequests from Cloudflare Workers
Allows setting cache_option_enabled compatibility flag as an alternative to updating the Compatibility Date
1 detail in Everything
Shard cache using custom cache key values
Nov 7, 2024
· release notes
Cloudflare adds cache sharding via custom cache keys using accept, referer, and user-agent headers.
Adds support for accept* headers (including accept, accept-encoding, accept-language) in custom cache keys to serve distinct cached versions based on content negotiation Adds referer header value to custom cache keys to cache content differently based on the referring page or site Adds user-agent header value to custom cache keys to maintain separate caches for different browsers, devices, or bots
3 details in Everything
Use Logpush for Email security user actions
Nov 7, 2024
· release notes
Logpush for Email security user actions allows routing audit logs to custom endpoints
Adds Logpush support for Email security user actions across Enterprise packages
1 detail in Everything
Cloudflare Workflows is now available in open beta for free and paid Workers plans, providing a programming model for reliable, long-running tasks triggered by events.
└──▷ USE IT
Scaffold a new long-running workflow project using the official starter template
shell
copy
npm create cloudflare@latest workflows-starter -- --template "cloudflare/workflows-starter"
Cloudflare's dashboard now allows creating URL rewrites using wildcard patterns through an intuitive interface.
New fields added to Gateway-related datasets in Cloudflare Logs
Oct 8, 2024
· release notes
Cloudflare Logs adds new fields to Gateway HTTP and Network datasets for enhanced visibility
Adds ApplicationIDs, ApplicationNames, CategoryIDs, CategoryNames, DestinationIPContinentCode, DestinationIPCountryCode, ProxyEndpoint, SourceIPContinentCode, SourceIPCountryCode, VirtualNetworkID, and VirtualNetworkName to Gateway HTTP logs Adds ApplicationIDs, ApplicationNames, DestinationIPContinentCode, DestinationIPCountryCode, ProxyEndpoint, SourceIPContinentCode, SourceIPCountryCode, TransportProtocol, VirtualNetworkID, and VirtualNetworkName to Gateway Network logs
2 details in Everything
Eliminate long-lived credentials and enhance SSH security with Cloudflare Access for Infrastructure
Oct 1, 2024
· release notes
Cloudflare introduces SSH with Access for Infrastructure, enabling short-lived certificates and MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone.
Enables fine-grained policy authoring for SSH access control, including specific ports, protocols, and SSH users. Provides infrastructure access monitoring via Access and SSH command logs.
2 details in Everything
Cloudflare makes Magic Network Monitoring free and accessible via Analytics & Logs for all account holders.
Enables free Magic Network Monitoring (MNM) for all Cloudflare accounts Adds Magic Monitoring entry under Analytics & Logs in the Cloudflare dashboard
2 details in Everything
Cloudflare AI Crawl Control adds AI Audit dashboard for monitoring and WAF WAF A reverse proxy that inspects HTTP/HTTPS traffic and blocks requests matching known attack patterns such as SQL injection or XSS, sitting between clients and a web application to filter malicious input before it reaches the server.
Adds AI audit dashboard to summarize crawling behavior of popular and known AI services Enables enforcing robots.txt policy via an automatic WAF rule
2 details in Everything
One-click Cache Rules templates now available
Sep 5, 2024
· release notes
Cloudflare introduces one-click Cache Rules templates for simplified CDN CDN A content delivery network, servers distributed across locations that cache and serve content near readers. It can reduce loading time and traffic to the original server.
Adds pre-configured cache rule templates available via the Rules > Templates dashboard section Provides Cache everything template to adjust the cache level for all requests Provides Bypass cache for everything template to bypass cache for all requests Provides Cache default file extensions template to replicate Page Rules caching behavior Provides Bypass cache on cookie template to bypass cache for requests containing specific cookies
+2 more
show less
Provides Set edge cache time template to cache responses with status code between 200 and 599 on the Cloudflare edge Provides Set browser cache time template to adjust how long a browser should cache a resource
7 details in Everything
New Rules Templates for One-Click Rule Creation
Sep 5, 2024
· release notes
Cloudflare introduces One-Click Rules Templates, allowing one-click deployment of pre-built rule configurations from a library.
Rules Templates feature enables one-click creation of common rule configurations using pre-built templates.Template cards are now available directly in the rule builder for each product.
2 details in Everything
Regionalized Generic Tiered Cache for higher hit ratios
Jul 19, 2024
· release notes
Cloudflare updates its caching infrastructure with regionalized generic tiered cache to improve hit ratios.
Enables higher cache hit ratios by routing content to designated upper-tier data centers within a region via consistent hashing.
1 detail in Everything
Cloudflare introduces capability to share user risk scores with Okta for security policy enrichment. This is an integration capability, not a vulnerability check or compliance rule.
Cloudflare Web Analytics adds a one-click toggle to exclude EU visitor data from Real User Monitoring
Adds a single click option in the Cloudflare dashboard to enable RUM RUM Real User Monitoring — a technique that collects performance and behaviour data from actual users' browsers or clients in production, giving cyber tools visibility into real-world latency and errors rather than synthetic test results.
1 detail in Everything
 changelog · Aug 2026
· source
· release history
 docs update · Oct 2026
· source
 docs update · Oct 2026
· source
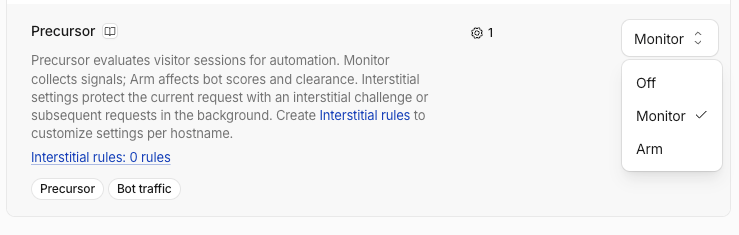 Bots - Precursor adds Monitor mode (2026-10-19) · Oct 2026
· source
· release history
 docs update · Oct 2026
· source
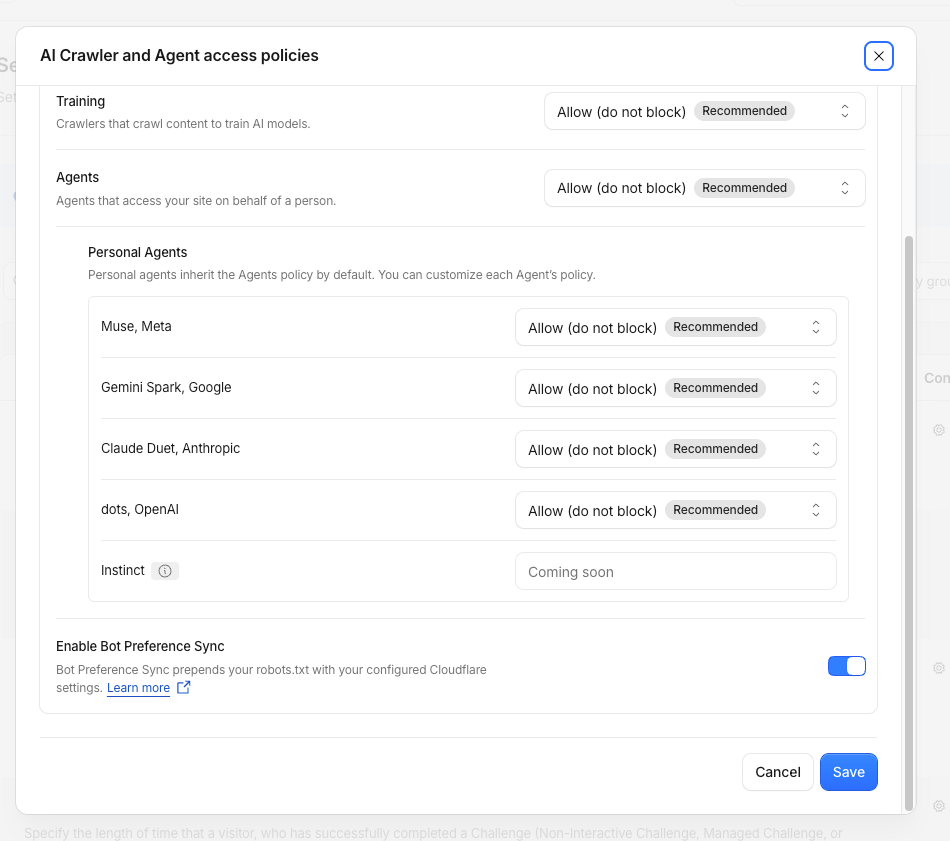 Bots - Granular access controls for the top Personal Agents (2026-11-04) · Nov 2026
· source
· release history
 Choose a badge style and copy the code →