DataDome
React Native SDK for Fetch 3.0.0 (2026-11-03) commercialThe section your link pointed to isn't on DataDome's page any more, so we've brought you to the top.
DataDome protects web, mobile, and API applications by detecting and blocking bot and fraud traffic.
import { DataDome } from '@datadome/react-native-core-datadome';
import { createDataDomeFetch } from '@datadome/react-native-datadome-fetch';

const dataDome = new DataDome({ clientKey: '<your-client-key>' });
const protectedFetch = createDataDomeFetch(dataDome);

// Use protectedFetch anywhere you would use fetch
const response = await protectedFetch('https://api.example.com/data');
{
  "eventDate": "2026-10-27T14:32:00Z",
  "...": "..."
}
{
  "serverSideKey": "<your-server-side-key>",
  "urlPatternInclusion": "/login|/checkout",
  "urlPatternExclusion": "/admin/",
  "enableGraphQLSupport": true,
  "graphQLEndpoint": "/graphql"
}
{
  "serverSideKey": "<your-server-side-key>",
  "enableMCPSupport": true,
  "mcpEndpoint": "/mcp,/mcp-v2",
  "maximumBodySize": 51200
}
{
  "clientSideKey": "<your-client-side-key>",
  "jsURL": "https://ddfoo.example.com/tags.js",
  "originURL": "https://origin.example.com",
  "maximumResponseBodySize": 4194304
}
<application
    android:enableOnBackInvokedCallback="true"
    ... />
DATADOME_URI_REGEX_EXCLUSION="/health|/heartbeat"
DATADOME_STATIC_ASSET_EXCLUSION="\.(css|gif|ico|jpg|js|png|svg|woff2)$"
DATADOME_REMOVE_MATRIX_PARAMS=false
DATADOME_URI_REGEX_EXCLUSION='/health|/heartbeat'
DATADOME_STATIC_ASSET_EXCLUSION=true
DATADOME_ENCODED_CHAR_INCLUSION=true
DATADOME_REMOVE_MATRIX_PARAMS=true
DATADOME_URI_REGEX_EXCLUSION="/health|/heartbeat"
DATADOME_STATIC_ASSET_EXCLUSION="\.(avi|avif|bmp|css|eot|flac|flv|gif|gz|ico|jpeg|jpg|js|json|less|map|mka|mkv|mov|mp3|mp4|mpeg|mpg|ogg|ogm|opus|otf|png|svg|svgz|swf|ttf|wav|webm|webp|woff|woff2|xml|zip)$"
DATADOME_URL_REGEX_EXCLUSION="/health|/heartbeat"
DATADOME_STATIC_ASSET_EXCLUSION=".(avi|avif|bmp|css|eot|flac|gif|gz|ico|jpeg|jpg|js|json|mp3|mp4|ogg|otf|png|svg|ttf|wav|webm|webp|woff|woff2|xml|zip)$"
# .env / Cloudflare Worker environment variables
DATADOME_URL_REGEX_EXCLUSION="/health|/heartbeat"
DATADOME_STATIC_ASSET_EXCLUSION="\.(avi|avif|bmp|css|eot|flac|gif|gz|ico|jpeg|jpg|js|json|less|map|mp3|mp4|png|svg|ttf|woff|woff2|xml|zip)$"
DATADOME_STATIC_ASSET_EXCLUSION = true
DATADOME_URL_REGEX_EXCLUSION = "^/api/internal/.*"
datadome_graphql_endpoint = graphql,api/graphql,query
datadome_use_x_forwarded_host = true
async fetch(
  request: Request,
  env: Env,
  ctx: ExecutionContext,
): Promise<Response> {
  const response = await dataDomeHandler.fetch(request as any, env, ctx);
  console.log(
    Object.entries(ctx.dataDomeEnrichedHeaders)
      .map(([name, value]) => `${name}: ${value}`)
      .join(' - '),
  );
  return response;
}
# Before (2.x)
DomeURIRegexExclusion="/health|/heartbeat|\.(css|js|png|gif|jpg)$"

# After (3.0)
DomeURIRegexExclusion="/health|/heartbeat"
DomeStaticAssetExclusion="\.(css|js|png|gif|jpg)$"
{
  graphQLEndpoint: '/api/graphql'
}
DATADOME_GRAPHQL_ENDPOINT=/api/graphql
DATADOME_MCP_ENDPOINT=/api/mcp
GraphQLEndpoint: "/api/graphql"
GraphQLEndpoint: /api/graphql
if request_headers['x-datadome-clientid'] ~= nil then
  body['ClientID'] = request_headers['x-datadome-clientid']
  datadomeHeaders["X-DataDome-X-Set-Cookie"] = "true"
else
  body['ClientID'] = clientId
end
datadome_mcp_endpoint = "/mcp"
resource "datadome_custom_rule" "agentic_login_rate_limit" {
  name          = "Rate-limit agentic login"
  endpoint_type = "agentic-login"
  response      = "intent_based"
  policy        = "rate_limit"
}
resource "datadome_custom_rule" "agentic_cart_timebox" {
  name          = "Time-box agentic cart abuse"
  endpoint_type = "agentic-cart"
  response      = "device_check"
  policy        = "time_box"
}
Summary
DataDome is a commercial web-app-security platform that detects and blocks bot traffic, account fraud, and L7 DDoSDDoSDistributed Denial of Service: an attack that floods a target system with traffic from many sources simultaneously, exhausting its resources so legitimate requests cannot be served. attacks across websites, mobile apps, and APIs. It runs as a service, deployed through server-side modules (Envoy, Apache, Fastly Compute) or client-side SDKs, with a request sent to DataDome's detection engine and a decision returned to allow or challenge it. It's aimed at application security and infrastructure teams protecting login, checkout, and API endpoints rather than at auditors or pentesters, and it now extends that coverage to agentic AI traffic, with endpoint types and challenge responses built for agent-driven logins, carts, and payments, plus GraphQL and MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. endpoint configuration. Launched in 2015, it ships releases regularly, most recently 14 days ago.
DataDome protects web, mobile, and API applications by detecting and blocking bot and fraud traffic.
How DataDome helps
Which requests hitting my login, checkout, or API endpoints are bots rather than real users?
sends the request's metadata to the detection engine and returns an allow-or-challenge decision that your integration enforces at the edge
Is the traffic hitting my agentic endpoints a real AI agent or a credential-stuffing script?
lets you classify traffic by agentic endpoint type (login, cart, payment, forms, account creation) and apply a rate-limit, time-box, or device-check response tuned to that flow
Can I see why a given request was challenged after the fact?
exposes the challenge type in the event payload and the response page, so downstream logs and handlers show which check triggered rather than just a pass/fail
Are my GraphQL or MCP endpoints actually being inspected?
reads the configured GraphQL and MCP endpoint paths (or your custom ones) to extract operation name and type instead of only checking the default routes
Can I correlate a blocked or challenged request with my own access logs?
writes DataDome's enriched detection headers into dynamic metadata under your tenant's namespace, so referencing that namespace in your access-log config surfaces bot-detection signals alongside the rest of the request
Am I stopping a burst of automated activity before it exhausts a limit?
applies rate-limit and time-box policy options on custom rules so repeated requests within a threshold or rolling window get enforced automatically rather than passing through individually
Languages
Features
Built from DataDome's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
What DataDome offers you
- Client SDKs1
- MCP server1
- Natural-language query1
- REST API1
- SaaS deployment1
- User-defined detection rules1
No capabilities match.
Bot Detection and Request Decisioning 4 capabilities DataDome's core function is evaluating incoming requests against its bot detection engine and returning allow, block, or challenge decisions. This covers the fundamental inspection pipeline that all other capabilities feed into.
Request validation API shipped Submits incoming request metadata to DataDome's detection engine and returns a decision on whether to allow, challenge, or block the request.
Also counts toward: REST API
release
-
Adds optional
eventDatefield to the payload to specify the effective event time.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Fraud SDK Go v2.1.0 (2026-10-02) · Oct 2026 · source · release history -
Adds
AcceptLanguagefield to the DataDome API reference for passing the request's Accept-Language header to the detection engine. api-docs-c11305f974b4 · Aug 2026 · source · release history
docs
- Time Status User Agent Retrieving recent requests… Loading… The Validate Request API checks incoming traffic against DataDome's bot detection engine. Your integration sends request metadata to DataDome, and we return a decision: allow or challenge. docs update · Jul 2026 · source
Envoy dynamic metadata enrichment shipped Writes DataDome's detection signals into Envoy's metadata layer so downstream services and observability tools can consume them.
release
- Adds enriched headers in context to enable log enhancement across all requests. Cloudflare Worker module 2.7.0 (2026-08-17) · Aug 2026 · source · release history
- Adds DataDome enriched headers to Envoy dynamic metadata, making bot-detection signals available for use in access logs and observability pipelines. Envoy module 2.7.0 (2026-07-21) · Jul 2026 · source · release history
docs
-
Logging The enriched headers returned by the Protection API are stored in Envoy dynamic metadata under the namespace <
DATADOME_TENANT_NAME>-datadome(for example default-datadome ). You can add them to your access logs by referencing that namespace in your access_log configuration. docs update · Jul 2026 · source
HTTP message signature collection shipped Collects HTTP message signature headers from requests to support cryptographic verification of request authenticity.
release
- Collects Signature, Signature-Agent, and Signature-Input headers to support HTTP message signatures as defined by RFC 9421. Fastly Compute module 1.4.0 (2026-07-20) · Jul 2026 · source · release history
Skyfire payment header collection shipped Collects a payment identity header from requests so it can be factored into bot detection decisions.
release
- Collects Skyfire-Pay-ID header from incoming requests. Fastly Compute module 1.4.0 (2026-07-20) · Jul 2026 · source · release history
Automated Threat and Abuse Prevention 3 capabilities DataDome identifies and responds to specific automated attack patterns such as credential stuffing, agentic AI misuse, and other bot-driven abuse across sensitive endpoints. Operators can configure policies to throttle or block these threats.
Custom rule policy enforcement shipped Lets operators build custom rules with threshold and time-window conditions and choose from an expanded set of enforcement responses.
release 9 total
- Asynchronous validate and collect calls are no longer supported Fraud SDK .NET 2.0.0 · Sep 2026 · source · release history
-
Adds
ValidateCustomandCollectCustommethods to support submitting custom event payloads Fraud SDK .NET 2.0.0 · Sep 2026 · source · release history - Replaces hard-coded HTTP status codes with values sourced from DataDome Protection API response headers, enabling dynamic status code handling for upcoming features. Nginx Module 3.1.0 (2026-09-07) · Sep 2026 · source · release history
-
Adds
SecCHUAFullVersionListfield to the DataDome API reference for passing the Sec-CH-UA-Full-Version-List client hint header. api-docs-c11305f974b4 · Aug 2026 · source · release history - Adds Via field to the DataDome API reference for forwarding proxy chain information. api-docs-c11305f974b4 · Aug 2026 · source · release history
-
Adds
CustomFieldString1,CustomFieldString2, andCustomFieldString3fields to the DataDome API reference for sending arbitrary custom string data alongside detection requests. api-docs-c11305f974b4 · Aug 2026 · source · release history
docs
- 2.3.0 (2026-08-28) Remove hard-coded status codes in favor of DataDome Protection API response headers, enabling seamless support for upcoming features about 3 hours ago seen Aug 2026 · source
Agentic AI traffic targeting shipped Allows custom rules to specifically target agentic AI traffic hitting endpoints such as login, checkout, and account creation.
Also counts toward: User-defined detection rules
release
-
Adds six new
endpoint_typevalues for custom rules targeting agentic AI traffic:agentic-general,agentic-account-creation,agentic-login,agentic-cart,agentic-forms, andagentic-payment. DataDome Terraform provider v2.4.0 (2026-06-30) · Jun 2026 · source · release history
example
-
Apply a time-box policy with a device_check response to block suspicious agentic cart activity within a rolling window.
resource "datadome_custom_rule" "agentic_cart_timebox" { name = "Time-box agentic cart abuse" endpoint_type = "agentic-cart" response = "device_check" policy = "time_box" }DataDome Terraform provider v2.4.0 (2026-06-30) · Jun 2026 · source
Credential-stuffing and automated agent throttling shipped Applies rate-limiting on login and other sensitive endpoints to slow down or stop automated credential-stuffing attacks.
example
-
Protect an agentic login endpoint with a rate-limit policy to throttle automated credential-stuffing agents.
resource "datadome_custom_rule" "agentic_login_rate_limit" { name = "Rate-limit agentic login" endpoint_type = "agentic-login" response = "intent_based" policy = "rate_limit" }DataDome Terraform provider v2.4.0 (2026-06-30) · Jun 2026 · source
Challenge and Response Handling 1 capability When DataDome's engine determines a request warrants friction, it can issue challenges to the client and adapt how those challenges are presented. This area covers the mechanics of surfacing and customising challenge interactions.
Challenge type awareness shipped Makes the specific type of challenge triggered available in event data and rendering functions so operators can tailor the user experience accordingly.
release
-
Accepts
challengeTypein thedisplayDataDomeResponsePagefunction, enabling style adaptation based on the challenge type being displayed. JavaScript Tag 5.9.0 (2026-07-20) · Jul 2026 · source · release history -
Adds
challengeTypeparameter to event payloads, exposing the type of challenge triggered in downstream event handling. JavaScript Tag 5.9.0 (2026-07-20) · Jul 2026 · source · release history
Platform and Protocol Coverage 4 capabilities DataDome extends its detection capabilities across a range of client types, protocols, and emerging traffic patterns, ensuring protection is not limited to standard browser HTTP traffic. This includes mobile SDKs, GraphQL clients, and AI agent protocols.
Custom GraphQL endpoint configuration shipped Lets operators declare a custom path for their GraphQL endpoint when it differs from the default route.
release 8 total
-
Adds
datadome_graphql_endpointconfig option to define one or more paths (comma-separated) used to detect GraphQL requests, defaulting tographql. Tyk module 1.4.0 (2026-08-24) · Aug 2026 · source · release history - Adds GraphQL support to the Envoy module. Envoy module 2.8.0 (2026-08-21) · Aug 2026 · source · release history
-
Adds
datadome_graphql_endpointconfiguration parameter to specify the GraphQL endpoint (defaults tographql). OpenResty module 1.7.0 (2026-08-18) · Aug 2026 · source · release history -
Adds
datadome_graphql_max_body_sizeconfiguration parameter to limit the request body size parsed for GraphQL requests. OpenResty module 1.7.0 (2026-08-18) · Aug 2026 · source · release history -
Adds
DATADOME_GRAPHQL_ENDPOINTparameter to specify the GraphQL endpoint (defaults to/graphql). Cloudflare Worker module 2.7.0 (2026-08-17) · Aug 2026 · source · release history -
Adds
graphQLEndpointparameter to specify the path(s) for the GraphQL endpoint, defaulting to/graphql. Node.js module 2.6.0 (2026-08-17) · Aug 2026 · source · release history
docs
-
ENABLE_GRAPHQL_SUPPORTEnables the support of GraphQL requests.GRAPHQL_ENDPOINT/graphqlGraphQL endpoint on which the operation name and type should be extracted. You can specify several endpoints separated with commas. FAQ How can I enable GraphQL support? docs update · Aug 2026 · source -
2.7.0 (2026-08-17) Add enriched headers in context to allow logs enhancement on all requests Introduce
DATADOME_GRAPHQL_ENDPOINTparameter to specify the GraphQL Endpoint (defaults to/graphqlIntroduceDATADOME_MCP_ENDPOINTparameter to specify the MCP Endpoint (defaults to/mcpabout 23 hours ago docs update · Aug 2026 · source - graphQLEndpoint GraphQL endpoint on which the operation name and type should be extracted. You can specify several endpoints separated with commas mcpEndpoint MCP endpoint on which the information should be extracted. You can specify several endpoints separated with commas. docs update · Aug 2026 · source
example
-
Route GraphQL traffic detection across multiple non-standard endpoints in a Tyk plugin config.
datadome_graphql_endpoint = graphql,api/graphql,queryTyk module 1.4.0 (2026-08-24) · Aug 2026 · source -
Override the default GraphQL and MCP endpoints when your app exposes them at non-standard paths.
DATADOME_GRAPHQL_ENDPOINT=/api/graphql DATADOME_MCP_ENDPOINT=/api/mcpCloudflare Worker module 2.7.0 (2026-08-17) · Aug 2026 · source -
Override the default GraphQL path when your API mounts GraphQL at a non-standard route.
{ graphQLEndpoint: '/api/graphql' }Node.js module 2.6.0 (2026-08-17) · Aug 2026 · source
Model Context Protocol (MCP) traffic inspection shipped Inspects traffic arriving on Model Context Protocol endpoints by letting operators define the MCP endpoint path in their integration.
release
-
Adds
datadome_enable_mcp_supportproperty to the Magento module configuration to enable MCP support. Magento module 1.2.247 (2026-08-19) · Aug 2026 · source · release history -
Adds
DATADOME_MCP_ENDPOINTparameter to specify the MCP endpoint (defaults to/mcp). Cloudflare Worker module 2.7.0 (2026-08-17) · Aug 2026 · source · release history -
Adds
mcp_endpointattribute toDataDomeMiddlewareto specify a custom MCP endpoint path (defaults to/mcp). Python ASGI module 1.2.0 (2026-07-28) · Jul 2026 · source · release history -
Adds Model Context Protocol (MCP) support with new
datadome_mcp_endpointconfiguration parameter (defaults to/mcp) to specify the MCP endpoint. Fastly Compute module 1.4.0 (2026-07-20) · Jul 2026 · source · release history
docs
-
DATADOME_GRAPHQL_ENDPOINTGraphQL endpoint on which the operation name and type should be extracted. You can specify several endpoints separated with commas.DATADOME_MCP_ENDPOINTMCP endpoint on which the information should be extracted. You can specify several endpoints separated with commas.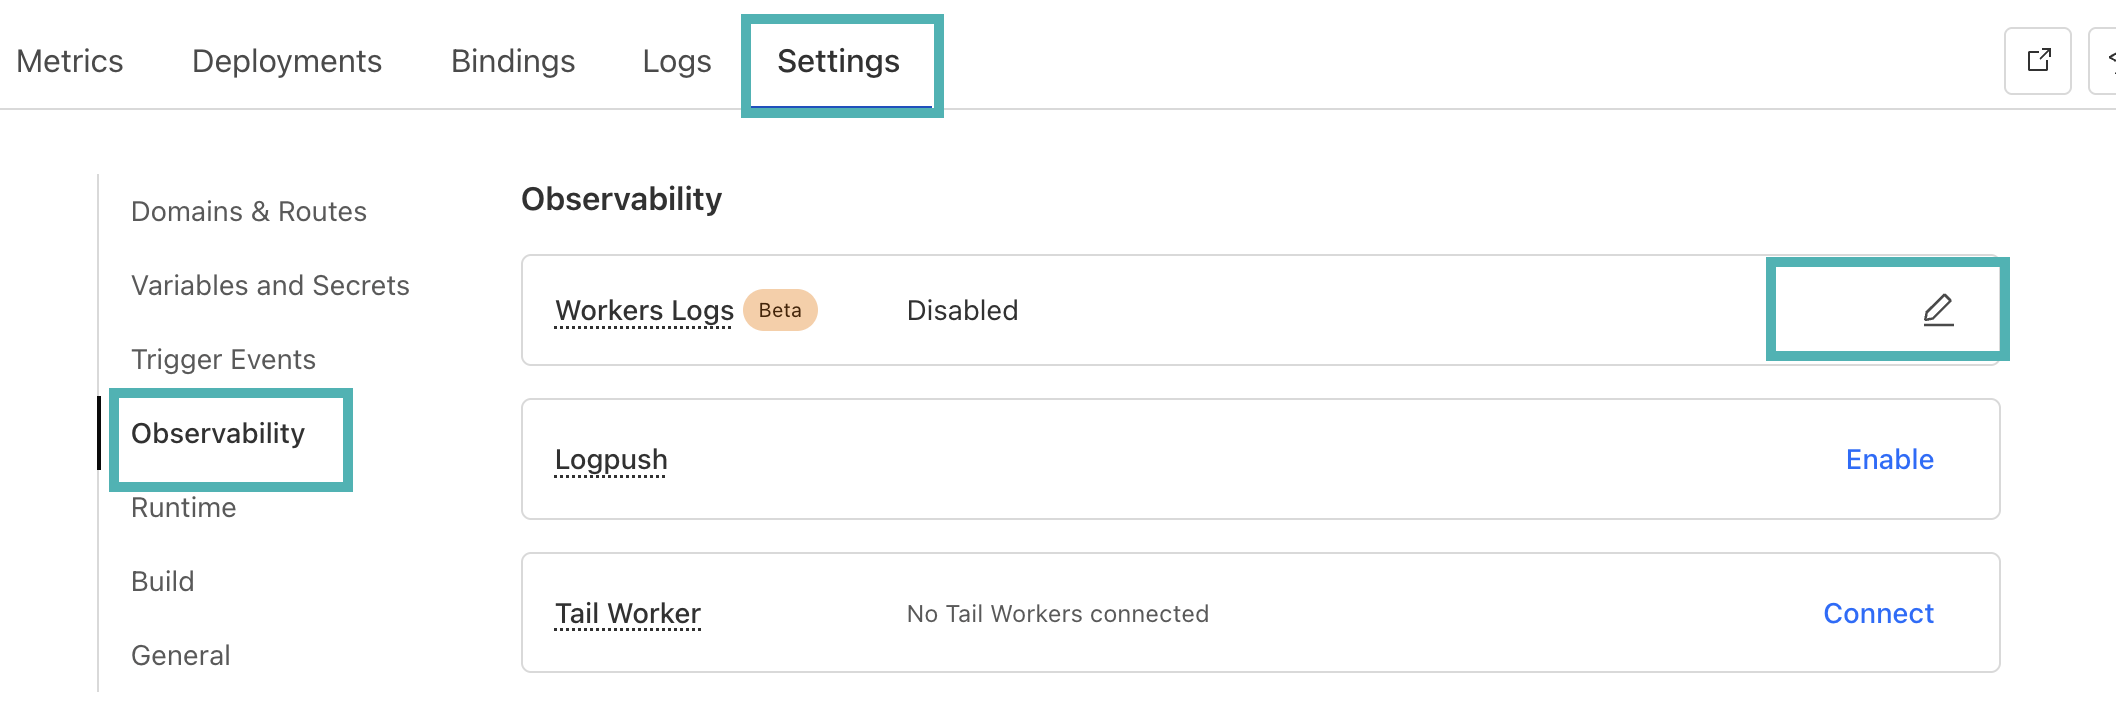 docs update · Aug 2026
· source
-
DATADOME_GRAPHQL_ENDPOINTGraphQL endpoint on which the operation name and type should be extracted. You can specify several endpoints separated with commas.DATADOME_MCP_ENDPOINTMCP endpoint on which the information should be extracted. You can specify several endpoints separated with commas. docs update · Aug 2026 · source -
DATADOME_GRAPHQL_ENDPOINTGraphQL endpoint on which the operation name and type should be extracted. You can specify several endpoints separated with commas.DATADOME_MCP_ENDPOINTMCP endpoint on which the information should be extracted. You can specify several endpoints separated with commas.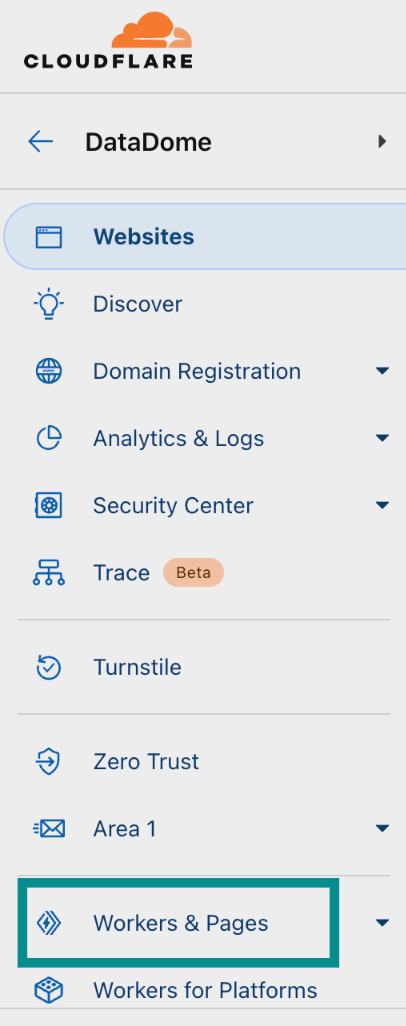 docs update · Aug 2026
· source
Apollo v2 GraphQL iOS bot protection shipped Brings DataDome's bot protection to iOS applications that use the Apollo v2 GraphQL client.
release
- Adds Swift Package Manager (SPM) support for iOS native dependencies alongside existing CocoaPods support; apps on Flutter 3.44+ with SPM enabled resolve the plugin via SPM automatically.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Flutter Dio SDK 3.5.0 (2026-10-02) · Oct 2026 · source · release history
-
Adds an iOS privacy manifest (
PrivacyInfo.xcprivacy) to the plugin. Flutter Dio SDK 3.5.0 (2026-10-02) · Oct 2026 · source · release history -
Adds
datadome_use_x_forwarded_hostconfig option to support host override via the X-Forwarded-Host header. Tyk module 1.4.0 (2026-08-24) · Aug 2026 · source · release history - Supports Apollo v2 GraphQL client for iOS, enabling DataDome bot protection on Apollo v2-based apps. iOS SDK for Apollo 4.0.0 (2026-06-30) · Jun 2026 · source · release history
example
-
Enable host override via the X-Forwarded-Host header when DataDome sits behind a reverse proxy that rewrites the Host.
datadome_use_x_forwarded_host = trueTyk module 1.4.0 (2026-08-24) · Aug 2026 · source
Extended DataDome cookie capacity shipped Increases the storage capacity of the DataDome cookie to support a larger set of detection signals and future features.
release
- Increases DataDome cookie length limit from 128 to 512 characters to support future capabilities. Python ASGI module 1.2.0 (2026-07-28) · Jul 2026 · source · release history
Other 15 capabilities
React Native fetch SDK shipped Provides a client-based API for React Native apps that wraps fetch to automatically add DataDome headers and handle bot challenges natively, with TypeScript support and graceful fallback on SDK errors.
Also counts toward: Client SDKs
release 12 total
-
The
datadomeper-request option is removed; the returned fetch function now applies DataDome headers and challenge checks to every request automatically. React Native SDK for Fetch 3.0.0 (2026-11-03) · Nov 2026 · source · release history -
Replace
DataDomeFetchand theDataDomesingleton (DataDome.configure,DataDome.getInstance) with createDataDomeFetch(dataDome), which takes aDataDomeclient created with new DataDome({ clientKey }) and returns afetch-compatiblefunction that automatically adds DataDome headers to every request and checks… React Native SDK for Fetch 3.0.0 (2026-11-03) · Nov 2026 · source · release history -
Re-export
DataDome,ResponseValidationStatus,DataDomeConfiguration, andDataDomeCookiefrom@datadome/react-native-core-datadome. React Native SDK for Fetch 3.0.0 (2026-11-03) · Nov 2026 · source · release history -
Accept a
string,URL, or Request as fetch input, and a Headers object, an array of pairs, or a plain object as headers. React Native SDK for Fetch 3.0.0 (2026-11-03) · Nov 2026 · source · release history -
DataDomeModal,DataDomeModule, andenableVerboseLogsare removed. React Native SDK for Fetch 3.0.0 (2026-11-03) · Nov 2026 · source · release history -
The
react-native-webviewpeer dependency is removed; challenges are now presented natively by the CoreDataDome SDK. React Native SDK for Fetch 3.0.0 (2026-11-03) · Nov 2026 · source · release history
example
-
Initialize DataDome protection for all fetch calls in a React Native app using the new client-based API.
import { DataDome } from '@datadome/react-native-core-datadome'; import { createDataDomeFetch } from '@datadome/react-native-datadome-fetch'; const dataDome = new DataDome({ clientKey:…React Native SDK for Fetch 3.0.0 (2026-11-03) · Nov 2026 · source
Static asset processing exclusion shipped Allows excluding specific file types such as images, videos, and stylesheets from bot detection processing.
release
-
Supports excluding static assets (e.g.,
avi,css,js,jpg,png,svg,mp4,woff2,zip, and dozens more) from DataDome processing via an exclusion list.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ api-docs-9a79fd98bf10 · Sep 2026 · source · release history -
Supports excluding static asset file types (including
avi,avif,bmp,css,eot,flac,flv,gif,gz,ico,jpeg,jpg,js,json,less,map,mka,mkv,mov,mp3,mp4,mpeg,mpg,ogg,ogm,opus,otf,pdf,png,svg,svgz,swf,tif,tiff,ttf,wav,… api-docs-d864889da5bc · Sep 2026 · source · release history
docs 7 total
-
This guide will help you navigate through changes included in version 3 of the DataDome CloudFront Node.js module for a successful upgrade. Split exclusion settings Move any static-asset extensions out of
DATADOME_URI_REGEX_EXCLUSION:DATADOME_URI_REGEX_EXCLUSIONnow holds only your own URL exclusions. docs update · Sep 2026 · source - Ability to exclude static assets (e.g., .css, .js, .jpg, etc.) from DataDome processing. List of static assets you have to exclude : avi|avif|bmp|css|eot|flac|flv|gif|gz|ico|jpeg|jpg|js|json|less|map|mka|mkv|mov|mp3|mp4|mpeg|mpg|ogg|ogm|opus|otf|pdf|png|svg|svgz|swf|tif|tiff|ttf|wav|webm|webp|woff|woff2|xml|zip 7 days… seen Sep 2026 · source
- Ability to exclude static assets (e.g., .css, .js, .jpg, etc.) from DataDome processing. List of static assets you have to exclude : avi|avif|bmp|css|eot|flac|flv|gif|gz|ico|jpeg|jpg|js|json|less|map|mka|mkv|mov|mp3|mp4|mpeg|mpg|ogg|ogm|opus|otf|pdf|png|svg|svgz|swf|tif|tiff|ttf|wav|webm|webp|woff|woff2|xml|zip 6 days… docs update · Sep 2026 · source
- Ability to exclude static assets (e.g., .css, .js, .jpg, etc.) from DataDome processing. List of static assets you have to exclude : avi|avif|bmp|css|eot|flac|flv|gif|gz|ico|jpeg|jpg|js|json|less|map|mka|mkv|mov|mp3|mp4|mpeg|mpg|ogg|ogm|opus|otf|pdf|png|svg|svgz|swf|tif|tiff|ttf|wav|webm|webp|woff|woff2|xml|zip 5 days… docs update · Sep 2026 · source
- Ability to exclude static assets (e.g., .css, .js, .jpg, etc.) from DataDome processing. List of static assets you have to exclude : avi|avif|bmp|css|eot|flac|flv|gif|gz|ico|jpeg|jpg|js|json|less|map|mka|mkv|mov|mp3|mp4|mpeg|mpg|ogg|ogm|opus|otf|pdf|png|svg|svgz|swf|tif|tiff|ttf|wav|webm|webp|woff|woff2|xml|zip 4 days… api-docs-b6ca6b54f992 · Sep 2026 · source
- Ability to exclude static assets (e.g., .css, .js, .jpg, etc.) from DataDome processing. List of static assets you have to exclude : avi|avif|bmp|css|eot|flac|flv|gif|gz|ico|jpeg|jpg|js|json|less|map|mka|mkv|mov|mp3|mp4|mpeg|mpg|ogg|ogm|opus|otf|pdf|png|svg|svgz|swf|tif|tiff|ttf|wav|webm|webp|woff|woff2|xml|zip 3 days… api-docs-9a79fd98bf10 · Sep 2026 · source
Android native SDK packaging shipped Packages the Android native SDK with support for predictive back gesture control via a BackBehaviour enum, with minimum requirements of androidx.activity 1.6.1 and compileSdk 33 or higher.
release
-
Requires
androidx.activity1.6.1 andcompileSdk33 or higher. Android SDK 3.1.0 (2026-10-21) · Oct 2026 · source · release history -
The SDK now requires
androidx.activity1.6.1 and apps must compile withcompileSdk33 or higher; projects on lower compile SDK versions will fail to build. Android SDK 3.1.0 (2026-10-21) · Oct 2026 · source · release history -
Adds support for Android predictive back gesture via
BackBehaviourenum (BLOCKED,GO_BACKGROUND,GO_BACK), honoured on Android 13+ when the app setsandroid:enableOnBackInvokedCallback="true"or targets API 36+.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Android SDK 3.1.0 (2026-10-21) · Oct 2026 · source · release history
example
-
Opt in to Android predictive back so DataDome's BackBehaviour controls what happens when a user swipes back on a protected screen.
<application android:enableOnBackInvokedCallback="true" ... />Android SDK 3.1.0 (2026-10-21) · Oct 2026 · source
AI Key Takeaways for threat reporting shipped Provides real-time AI-generated summaries of threat data on the DataDome homepage and trend reports, with a security analyst view covering detection precision and attack patterns and a business view reframing the same data for executive audiences.
release
-
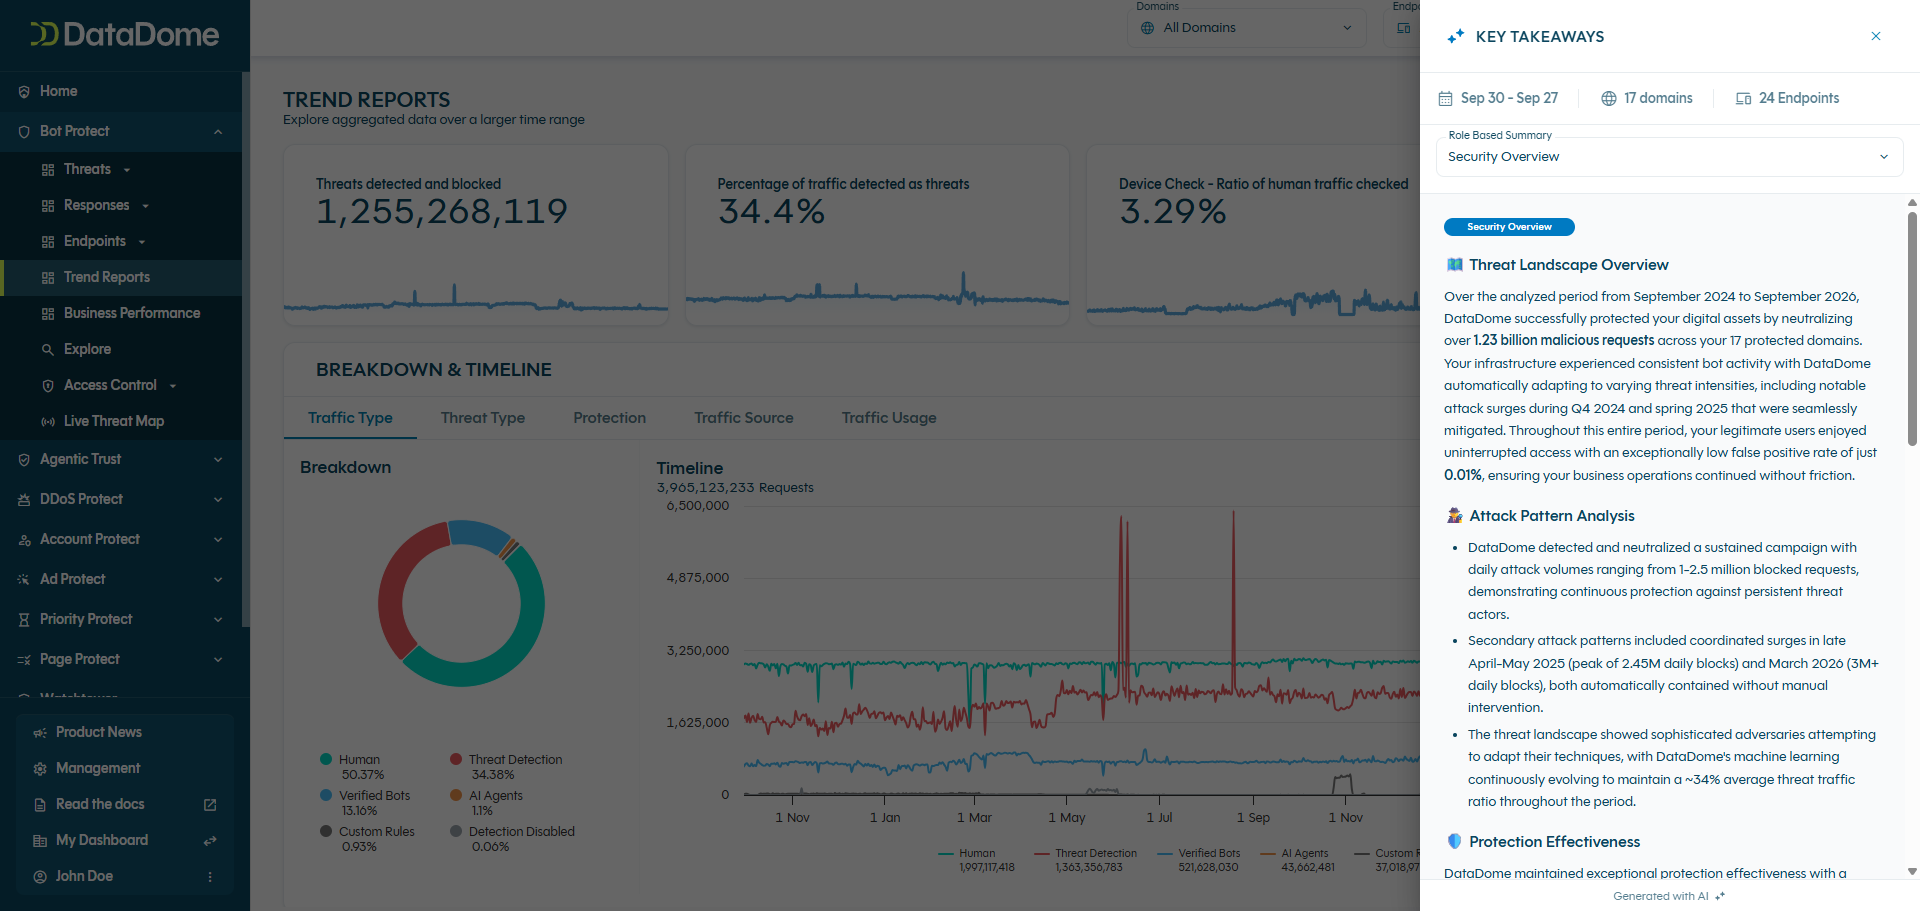
Adds AI Key Takeaways to the DataDome Homepage & Trend Reports, providing a real-time AI-generated summary of threat data including sophisticated bots, AI agents, and threat traffic ratio.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
 announced · Oct 2026
· source
· release history
- Introduces a business view toggle within AI Key Takeaways that reframes the same underlying data for executive audiences, covering protection status, threats blocked, false positive rates, and actionable guidance for internal reporting. announced · Oct 2026 · source · release history
- Introduces a security view as the default mode of AI Key Takeaways, surfacing detection precision, critical escalations, unusual behavioral patterns, attack pattern analysis, and configuration recommendations. announced · Oct 2026 · source · release history
example
-
Switch from the security analyst view to the executive business view inside AI Key Takeaways to prepare a monthly risk report without rebuilding data from scratch.
In the DataDome dashboard, go to Homepage or Trend Reports > AI Key Takeaways > toggle from 'Security view' to 'Business view'.announced · Oct 2026 · source
Fraud event timestamp override shipped Allows operators to specify an optional `eventDate` field when submitting fraud events to set the effective event time.
release
-
Adds optional
eventDatefield to the payload to specify the effective event time.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Fraud SDK .Net 2.1.0 (2026-10-27) · Oct 2026 · source · release history -
Adds optional
eventDatefield to specify the effective event time when submitting fraud events.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Fraud SDK Java 3.1.0 (2026-10-21) · Oct 2026 · source · release history
example
-
Pass
eventDatein a fraud event payload to record the actual time an event occurred rather than the submission time — useful for replaying or backfilling events.{ "eventDate": "2026-10-27T14:32:00Z", "...": "..." }Fraud SDK .Net 2.1.0 (2026-10-27) · Oct 2026 · source
iOS native SDK packaging shipped Packages the iOS native SDK with Swift Package Manager support alongside CocoaPods, an updated deployment target, and an Apple privacy manifest.
release
- Raises the iOS deployment target Flutter Dio SDK 3.5.0 (2026-10-02) · Oct 2026 · source · release history
-
Adds an iOS privacy manifest (
PrivacyInfo.xcprivacy) Flutter Dio SDK 3.5.0 (2026-10-02) · Oct 2026 · source · release history - Adds Swift Package Manager (SPM) support for iOS native dependencies alongside existing CocoaPods support Flutter Dio SDK 3.5.0 (2026-10-02) · Oct 2026 · source · release history
Lambda@Edge response header forwarding documented Forwards headers on challenged responses to comply with the Lambda@Edge response format.
docs
- 3.0.1 (2026-09-29) headers forwarded on challenged responses to comply with the Lambda@Edge response format. about 5 hours ago seen Sep 2026 · source
- From Node.js runtime version 24 onward, callback-based function handlers have been removed and replaced by the async / await pattern. According to the supported runtimes list of AWS, the Node.js runtimes prior to this version will all be deprecated in April 2027. docs update · Sep 2026 · source
-
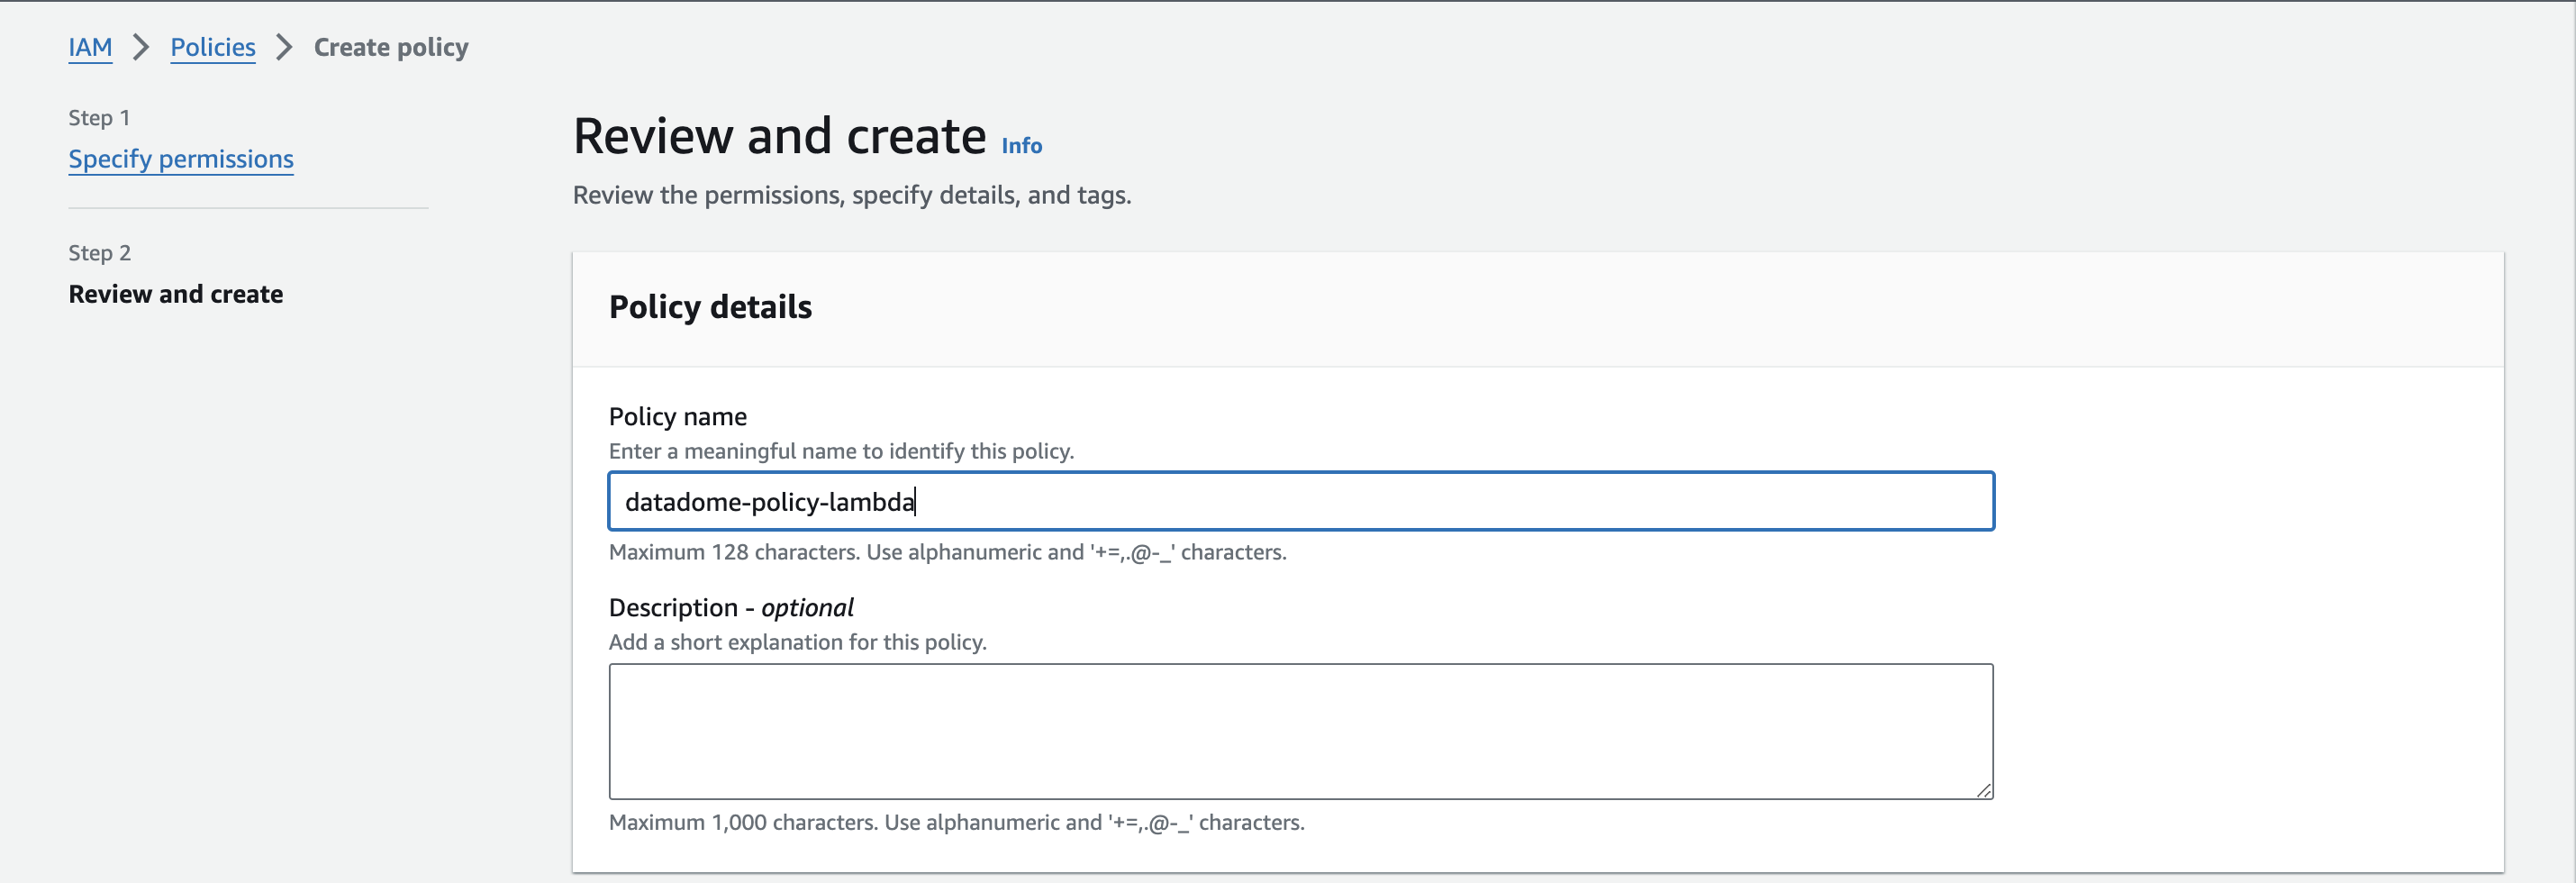
To update the code of the Lambda@Edge and publish a new version, apply the steps below. Refer to the changelog for details and the upgrade pages for breaking chages from v1 to v2 v2 to v3 5 days ago
 seen Sep 2026
· source
MCP Trend Report Querying shipped Enables MCP-compatible AI agents and agentic workflows to query automated traffic trends, threat types, scraping activity, and credential-stuffing patterns in natural language via a hosted MCP endpoint.
Also counts toward: MCP server, Natural-language query, SaaS deployment
release
- Enables AI agents to query automated traffic trends, threat types, scraping activity, and credential-stuffing patterns in natural language directly from tools like Slack-connected assistants, enterprise copilots, or custom agent pipelines. announced · Aug 2026 · source · release history
- New hosted MCP server exposes DataDome Trend Reports data to MCP-compatible AI agents and agentic workflows, authenticated via existing DataDome credentials — no custom integration or infrastructure required. announced · Aug 2026 · source · release history
example
-
Connect an MCP-compatible AI agent to DataDome's hosted MCP endpoint to query Trend Reports in natural language from within existing workflows.
In your MCP-compatible AI agent or tool, configure the server connection to DataDome's hosted MCP endpoint and authenticate using your existing DataDome credentials.announced · Aug 2026 · source
TLS JA3/JA4 fingerprinting shipped Captures TLS handshake fingerprints using the JA3 and JA4 standards for bot detection.
release
- DataDome now collects TLS fingerprints from incoming requests to send richer bot-detection signals to the Bot Protect API.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Node.js module 2.7.0 (2026-10-28) · Oct 2026 · source · release history
-
JA3andJA4TLS fingerprints Google Cloud Load Balancer module 1.8.0 · Sep 2026 · source · release history
Azion edge platform integration shipped Provides native DataDome bot and fraud protection for the Azion edge platform, supporting both server-side and client-side integrations via Azion Functions.
release
- Adds native DataDome bot and fraud protection integration for the Azion edge platform.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Azion module 1.0.0 (2026-10-21) · Oct 2026 · source · release history
docs
- This module intends to be used with Azion Functions . This documentation describes both server-side and client-side integrations. docs update · Oct 2026 · source
TypeScript type definitions shipped Provides TypeScript type definitions for DataDome request metadata, including the RequestMetadata property.
release
-
DataDome now includes the
RequestMetadataproperty in the TypeScript type definitions. Node.js module 2.7.0 (2026-10-28) · Oct 2026 · source · release history
Cloudflare Workers edge integration shipped Adds DataDome bot-protection support to Cloudflare Workers via the `datadome-cloudflare-worker` Rust crate.
release
-
Adds the
datadome-cloudflare-workerRust crate for integrating DataDome bot protection natively inside Cloudflare Workers.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Cloudflare Worker Rust module 1.0.0 (2026-10-27) · Oct 2026 · source · release history
Fastly Compute edge integration shipped Adds DataDome bot-protection support to Fastly Compute edge services via the `datadome-fastly-compute` Rust crate.
release
-
Introduces the
datadome-fastly-computeRust crate, adding DataDome bot-protection support to Fastly Compute edge services.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Fastly Compute Rust module 1.0.0 (2026-10-21) · Oct 2026 · source · release history
.NET 8.0 platform support shipped Adds support for the .NET 8.0 runtime environment.
release
-
Adds
.NET 8.0platform support Fraud SDK .NET 2.0.0 · Sep 2026 · source · release history
Replay challenge cookie management documented Ensures replay cookies are isolated per request so a leftover cookie from a previous request does not affect unrelated traffic, and clears the cookie only after the original request has been successfully replayed.
docs
- 1.3.1 (2026-09-29) Fix the replay feature so a leftover cookie from a previous request no longer affects unrelated traffic Fix the replay cookie so it is only cleared after the original request has been successfully replayed Fix an edge case where the replay cookie could be set even though the challenge page did not… seen Sep 2026 · source
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Screenshots
From the release notes, newest first. Click one to see it full size.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for DataDome, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail DataDome puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Website history
datadome.co, every changeDataDome's home page and 1 more page as they looked each month from September 2021 to October 2026: 13 renders, 6 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Coverage
Missing something? Tell us
What DataDome connects to, runs on and detects, read from its release notes and docs. So far: 3 new integrations.
3 changes, tracked since Oct 21, 2026.
-
Oct 272026
new DataDome Cloudflare Workers integration (Rust)
Add initial datadome-cloudflare-worker crate for Cloudflare Workers
-
Oct 212026
new Fastly Compute (Rust) integration
With datadome-fastly-compute
Add initial datadome-fastly-compute crate for Fastly Compute
-
Oct 212026
new DataDome Azion module
Initial release
Cloud platforms & services 4
Other 1
Nothing first seen in this window. That doesn't mean DataDome shipped nothing, only that we found no record of it.
How we count
Read from 9 of 62 release notes and docs updates we hold for DataDome. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through DataDome's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
62 entries
No entries match these filters.
- November 20261
- October 202611
- September 202618
- August 202622
- July 20268
- June 20262
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →