No entries match these filters. Clear filters
Veracode adds async Fire-and-Forget remediation, Domain field for DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces. GDPR GDPR EU regulation enacted in 2018 that governs how organizations collect, store, and process personal data of EU residents, giving cyber tools legal obligations around data handling and breach notification. NIS2 NIS2 EU directive that expands mandatory cybersecurity requirements to more sectors and member states than its predecessor, giving cyber tools a compliance framework to map controls and reporting obligations against.
Veracode CLI v2.54.0 now supports asynchronous Fire-and-Forget (FnF) mode for the fix command, submitting remediation requests for background processing without waiting for fixes to be generated and pull requests to be created.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Configure an optional Domain field when setting up HTTP basic authentication for DAST web application scans, enabling authentication to applications that require domain-based credentials. Scans now collect compliance evidence for cookie consent tracking, third-party data flows, destination countries, and privacy, legal, and copyright documentation, supporting GDPR, NIS2, and DORA assessments. Static Analysis Engine v2026.10 now supports JDK 27. Static Analysis Engine v2026.10 now supports LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code.
+1 more
show less
Static Analysis Engine v2026.10 now supports Scala 3.9.
Veracode CLI v2.54.0 now supports asynchronous Fire-and-Forget (FnF) mode for the fix command, submitting remediation requests for background processing without waiting for fixes to be generated and pull requests to be created.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Configure an optional Domain field when setting up HTTP basic authentication for DAST web application scans, enabling authentication to applications that require domain-based credentials. Scans now collect compliance evidence for cookie consent tracking, third-party data flows, destination countries, and privacy, legal, and copyright documentation, supporting GDPR, NIS2, and DORA assessments. Static Analysis Engine v2026.10 now supports LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code.
2 more in Everything
Integration updates (2026-10-30)
Oct 30, 2026
·
issue 125
Veracode integrations add IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup.
Add a predependency_command parameter to veracode.yml in the GitHub, GitLab, and Azure DevOps Workflow Integrations to run commands before Veracode packages the project. New integration Add a build_runs_on parameter to veracode.yml in the GitHub Workflow Integration for SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. Add a policy parameter to veracode.yml in the GitHub, GitLab, and Azure DevOps Workflow Integrations for IaC scans. Add a custom agent pool name parameter to veracode.yml in the Azure DevOps Workflow Integration. Veracode Scan for VS Code now adds environment setup checks to identify connectivity, proxy, DNS, firewall, and TLS issues.
+6 more
show less
Veracode Scan for VS Code now adds a Mitigated Findings section to the Flaws That Violate Policy view, a Current File filter, and file-name grouping for Static Scan Findings. New integration GitHub Workflow Integration v2.0.0 now lets you install, configure, update, and schedule scans directly from the Veracode Platform.GitHub Workflow Integration v2.1.1 adds a new uninstallation workflow on the Veracode Platform. Java API wrapper v26.10.20.0 now automatically includes Git metadata in Static Analysis scans. Veracode Scan for Visual Studio v0.8.0 adds a Scan Scope setting and usage analytics. GitLab Workflow Integration now prevents merge requests from merging when break_build_policy_findings and break_build_on_error are both set to true.
11 details in Everything
└──▷ BREAKING ON UPGRADE
! Veracode Azure DevOps Extension v4.0.0 deprecates Veracode Flaw Importer v3 and replaces it with VeracodeFlawImporter v4; existing pipelines must be manually migrated from v3 to v4.! Java API wrapper v26.10.20.1 now updates the repository URL in the Veracode application profile only when -repourl is explicitly specified.
SAST updates (2026-10-28)
Oct 28, 2026
·
issue 124
Veracode SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment. veracode.json-based exclusions for Java .jar files and classes.
New supported platform Scan C# source code directly (Static Analysis Engine v2026.10).New supported platform New detection Scan Java source code and view it on the platform, using veracode.json to exclude specific .jar files or classes from analysis.New supported platform Pipeline Scan now accepts packaged artifacts larger than 200 MB with no changes to existing integrations.New integration Veracode SAST now integrates with DryRun Security, surfacing findings and remediation guidance during pull request and code review workflows.
4 details in Everything
Integration updates archive (2026-10-27)
Oct 27, 2026
·
issue 123
Veracode adds GitHub Workflow App for org-wide scanning, JetBrains SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
└──▷ TRY IT
Route all Veracode C# API Wrapper calls through a corporate proxy without modifying wrapper arguments.
copy
$ export https_proxy=http://proxyuser:proxypass@proxy.corp.example.com:8080 Control polling frequency for a long-running Upload and Scan in the Azure DevOps pipeline task to reduce API call overhead.
azure-pipelines.yml
copy
- task: Veracode@3
  inputs:
    ConnectionDetailsSelection: 'Endpoint'
    AnalysisService: 'VeracodeEndpoint'
    veracodeAppProfile: 'MyApp'
    version: '$(build.buildNumber)'
    filepath: 'drop/myapp.zip'
    scanpollinginterval: '60'
Adds scanpollinginterval and lifecyclestage as optional parameters to the Azure DevOps Extension Upload and Scan task (lifecyclestage is not supported in YAML).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds support for the -includenewmodules parameter to the Java API Wrapper. Supports proxies via the https_proxy environment variable in the C# API Wrapper 23.5.8.8, accepting host, port, and credentials. Enables sending requests to the Identity REST API from within the Java API Wrapper. Adds Dynamic Analysis scan statuses STOPPED_VERIFYING_PARTIAL_RESULTS and STOPPED_PARTIAL_RESULTS_AVAILABLE to the Java API Wrapper and Jenkins Plugin.
+5 more
show less
Adds a Show Unstable Status for Failed Policy Evaluation option to the Veracode Jenkins Plugin, marking a job as Unstable when a scan passes but fails security policy. Releases the Veracode GitHub Workflow App, enabling Static Analysis, SCA, and Container Security scans across thousands of GitHub repositories from a single centralized workflow location. Releases Veracode SCA Scan for JetBrains 0.6.0, a new extension integrating SCA into IntelliJ IDEA and PyCharm to detect vulnerabilities in open-source libraries, dependencies, and licenses. Adds an option to the Azure DevOps Extension Flaw Import task to configure importing findings from Static Analysis and SCA only, an option to overwrite the iteration path in work items of imported flaws, and an iteration path field to the Flaw Importer task work item settings (Azure DevOps Extension 3.23.0). Adds support for TSRV mitigations and .NET 7 in Veracode Static for Visual Studio 2019 and 2022 v1.9.0.
Adds scanpollinginterval and lifecyclestage as optional parameters to the Azure DevOps Extension Upload and Scan task (lifecyclestage is not supported in YAML).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Supports proxies via the https_proxy environment variable in the C# API Wrapper 23.5.8.8, accepting host, port, and credentials. Enables sending requests to the Identity REST API from within the Java API Wrapper. Adds a Show Unstable Status for Failed Policy Evaluation option to the Veracode Jenkins Plugin, marking a job as Unstable when a scan passes but fails security policy. Releases the Veracode GitHub Workflow App, enabling Static Analysis, SCA, and Container Security scans across thousands of GitHub repositories from a single centralized workflow location.
+1 more
show less
Releases Veracode SCA Scan for JetBrains 0.6.0, a new extension integrating SCA into IntelliJ IDEA and PyCharm to detect vulnerabilities in open-source libraries, dependencies, and licenses.
4 more in Everything
└──▷ BREAKING ON UPGRADE
! End of support for Team Foundation Server (TFS) in Veracode Azure DevOps Extension 3.24.0.
SAST updates archive (2026-10-27)
Oct 27, 2026
·
issue 123
Veracode SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment. --include module selection, and broad language/framework additions through 2023.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds --include parameter to Pipeline Scan to specify top-level modules to include during scanning, with prescan module discovery now shown in results; available in Veracode CLI version 23.4.3-0 and Veracode Docker image version 23.4.3.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Introduces a new COBOL scanner for Veracode Static Analysis with advanced pattern recognition and static analysis techniques for more accurate vulnerability detection in COBOL code. Adds support for Quarkus (Kubernetes-native Java stack for OpenJDK HotSpot and GraalVM) in static analysis. Adds support for Micronaut 3.8.x (JVM JVM The Java Virtual Machine, a runtime maintained by Oracle (and implemented by others) that executes Java bytecode on any OS, giving cyber tools a portable, garbage-collected environment with a large ecosystem of libraries. Adds .NET Minimal API support.
+5 more
show less
Adds PHP Laravel 10 support. Adds iOS 17 initial support. Adds Go 1.21 support. Adds AWS SDK for Go v2 support. Adds KMSKMS A managed service that creates, stores, rotates and controls access to encryption keys, usually backed by HSMs. Applications ask it to encrypt or decrypt rather than holding keys themselves.
Adds --include parameter to Pipeline Scan to specify top-level modules to include during scanning, with prescan module discovery now shown in results; available in Veracode CLI version 23.4.3-0 and Veracode Docker image version 23.4.3.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Introduces a new COBOL scanner for Veracode Static Analysis with advanced pattern recognition and static analysis techniques for more accurate vulnerability detection in COBOL code. Adds support for Quarkus (Kubernetes-native Java stack for OpenJDK HotSpot and GraalVM) in static analysis. Adds support for Micronaut 3.8.x (JVM JVM The Java Virtual Machine, a runtime maintained by Oracle (and implemented by others) that executes Java bytecode on any OS, giving cyber tools a portable, garbage-collected environment with a large ecosystem of libraries. Adds .NET Minimal API support.
+4 more
show less
Adds PHP Laravel 10 support. Adds iOS 17 initial support. Adds Go 1.21 support. Adds AWS SDK for Go v2 support.
1 more in Everything
└──▷ BREAKING ON UPGRADE
! Veracode deprecated support for .NET cleansers for flaw classes CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. antixsslibrary.dll: Microsoft.Security.Application.AntiXss.HtmlAttributeEncode, antixsslibrary.dll: Microsoft.Security.Application.AntiXssEncoder.HtmlAttributeEncode, antixsslibrary.dll: Microsoft.Security.Application.Encoder.HtmlAttributeEncode, antixsslibrary.dll: Microsoft.Security.Application.Encoder.HtmlEncode, mscorlib.dll: System.Security.SecurityElement.Escape, system.dll: System.Net.WebUtility.HtmlEncode, system.web.dll: System.Web.HttpServerUtility.HtmlEncode, system.web.dll: System.Web.Security.AntiXss.AntiXssEncoder.HtmlEncode, system.web.dll: System.Web.Util.HttpEncoder.HtmlAttributeEncode, system.web.dll: System.Web.Util.HttpEncoder.HtmlEncode, system.web.mvc.dll: System.Web.Mvc.HtmlHelper.AttributeEncode, system.web.mvc.dll: System.Web.Mvc.HtmlHelper.Encode, system.windows.browser.dll: System.Windows.Browser.HttpUtility.HtmlEncode, system.windows.dll: System.Net.HttpUtility.HtmlEncode, System.Runtime.dll: System.Net.WebUtility.HtmlEncode — applications relying on these as cleansers will no longer have those flaws suppressed.! Python applications with flaws previously reported as CWE-201 that should have been CWE-918 will be recategorized, potentially breaking existing flaw matching and requiring new mitigations.! All COBOL scans now use the upgraded scanner, which may identify additional vulnerabilities and impact flaw matching for existing applications.
CLI updates (2026-10-27)
Oct 27, 2026
·
issue 123
Veracode CLI v2.53.0 adds veracode scan static and veracode findings static commands plus a --csharp-source packaging flag.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Run a static scan inside a Git repo and immediately review findings without leaving the CLI — ideal for gating a PR before merge.
copy
$ veracode scan static && veracode findings static
Introduces several new commands: veracode scan static for running static scans and reviewing security findings within a Git workflow; veracode findings static for accessing cached static scan findings in the local Veracode directory; veracode package discover for detecting toolchains required to create scannable artifacts; veracode sca for SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. CycloneDX 1.6 CycloneDX 1.6 An OWASP-maintained Software Bill of Materials standard that catalogs components, dependencies, and supply-chain metadata; tools use it to produce or consume machine-readable SBOMs in a widely supported schema. SPDX 2.3 SPDX 2.3 An open standard from the Linux Foundation for describing software bills of materials, letting cyber tools exchange dependency, license, and vulnerability data in a common machine-readable format. auth login for onboarding new users via OAuth2 OAuth2 An open authorization framework (RFC 6749) that lets a service grant limited access to a user's resources on another service without exposing credentials, giving cyber tools a standard way to authenticate against third-party APIs. Adds several enhancements to veracode package: the --csharp-source flag to package C# source code directly for Static Analysis without compiling it into binaries; the --skip-packagers flag to exclude specific artifacts (such as unsupported SQL) from packaging results without affecting other languages; the --exclude flag to prevent specified Java packages or JAR files from being scanned; the VERACODE_PACKAGE_GOLANG_GENERATE environment variable to enable client-side CGO code generation when packaging Go applications; the SRCLR_MAKE_WINDOWS environment variable to support preprocessing C/C++ source files with Make on Windows using a native Windows gcc or clang compiler; the --java-source flag and VERACODE_PACKAGE_JAVA_SOURCE=true environment variable to enable Java source code packaging; support for requirements-dev.txt in Python packaging workflows to include development dependencies; support for the Poetry package management tool for Python autopackaging; automatic inclusion of .yaml, .yml, and .properties files when packaging Java source code; and support for packaging Go v1.24. Supports asynchronous Fire-and-Forget (FnF) mode in veracode fix sca, submitting remediation requests for background processing without waiting for fixes or pull requests. The veracode dynamic scan command now supports target UUIDs UUIDs A universally unique identifier, usually a 128-bit value used to identify an object across systems. It is designed to make independently generated identifiers unlikely to collide. veracode package discover now detects toolchains for JavaScript projects using npm or Yarn, provides toolchain detection for Java projects using the Gradle package manager, and introduces exit codes.
+3 more
show less
Introduces exit codes 5, 6, and 7 for veracode package to improve CI/CD pipeline automation and error handling. veracode scan now categorizes secret-type findings as Critical, prioritizes vulnerability results from the NVD NVD The National Vulnerability Database, maintained by NIST, is the U.S. government repository of CVE records enriched with CVSS scores and metadata; cyber tools query it to drive vulnerability prioritization. IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Adds support for generic packager for Apex in veracode package.
Introduces several new commands: veracode scan static for running static scans and reviewing security findings within a Git workflow; veracode findings static for accessing cached static scan findings in the local Veracode directory; veracode package discover for detecting toolchains required to create scannable artifacts; veracode sca for SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. CycloneDX 1.6 CycloneDX 1.6 An OWASP-maintained Software Bill of Materials standard that catalogs components, dependencies, and supply-chain metadata; tools use it to produce or consume machine-readable SBOMs in a widely supported schema. SPDX 2.3 SPDX 2.3 An open standard from the Linux Foundation for describing software bills of materials, letting cyber tools exchange dependency, license, and vulnerability data in a common machine-readable format. auth login for onboarding new users via OAuth2 OAuth2 An open authorization framework (RFC 6749) that lets a service grant limited access to a user's resources on another service without exposing credentials, giving cyber tools a standard way to authenticate against third-party APIs. Adds support for generic packager for Apex in veracode package.
6 more in Everything
DAST updates (2026-10-27)
Oct 27, 2026
·
issue 123
Veracode DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces. REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Adds an optional Domain field when configuring HTTP basic authentication for DAST web application scans, enabling authentication to applications that require domain-based credentials. Adds support for custom host-to-IP address mappings in DAST scans, configurable when DNS lookup is unavailable or not desired. New integration Enables assigning multiple teams to a DAST target when creating a web application or API specification, improving collaborative security ownership.Adds Directory Restrictions to DAST target configuration to control scan scope. Adds enhanced scheduling capabilities to the DAST Schedule feature, with advanced configuration options and greater flexibility for managing scan schedules.
+14 more
show less
Adds business unit selection when creating a web application or API specification target, or on the DAST configuration page. DAST now supports manual application linking to connect analysis run results to an application in the Veracode Platform for policy evaluation and combined multi-scan reporting. DAST Enterprise mode adds downloadable scan reports providing greater visibility into scan coverage and scanner behavior. DAST Enterprise mode adds an AI-assisted login authentication method, enabling coverage of complex login flows without recorded login scripts. ISM endpoint 24.10.0 introduces a proxy exclusion list, allowing specified hosts to bypass configured proxy settings. New supported platform The DAST Target Configuration Service REST API is now publicly available, enabling automation of DAST target management and analysis triggering.Web application and API scans now support time-based one-time password (TOTP TOTP A one-time password algorithm (RFC 6238) that generates short-lived codes from a shared secret and the current time, giving cyber tools phishing-resistant second-factor authentication without a server round-trip. multi-factor authentication multi-factor authentication Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. Web application and API scans now support custom cookies for authentication. Dynamic Analysis REST API now supports setting URL scan settings at the organization level for all analyses and scans. Adds a Manual Resume feature for Dynamic Analysis, enabling manually resuming a scheduled analysis from a paused state. API Scanning adds Scriptable Request Modification, using JavaScript to modify HTTP requests at runtime during authentication. Adds a similarity threshold setting for web application analyses to control ignoring of similar web pages during scanning. Dynamic Analysis now creates verification screenshots after 50 consecutive login failures, capturing when and where in the scanning process the failures occurred. Adds detailed historical information view for all past occurrences of dynamic analyses and their scans.
19 details in Everything
└──▷ BREAKING ON UPGRADE
! The DAST scheduling REST API endpoints have changed. Integrations using the REST API to manage DAST schedules must be updated to use the new endpoints as defined in the DAST API specification.
EASM updates (2026-10-26)
Oct 26, 2026
·
issue 121
EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do. KEV KEV CISA's Known Exploited Vulnerabilities catalog, a list of vulnerabilities with evidence of exploitation in real attacks. It helps teams prioritize fixes for problems attackers already use. GDPR GDPR EU regulation enacted in 2018 that governs how organizations collect, store, and process personal data of EU residents, giving cyber tools legal obligations around data handling and breach notification. NIS2 NIS2 EU directive that expands mandatory cybersecurity requirements to more sectors and member states than its predecessor, giving cyber tools a compliance framework to map controls and reporting obligations against.
Validates components against the EASM knowledge base so risk scores reflect real vulnerabilities per version, not just software age.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Collects compliance evidence for cookie consent tracking, third-party data flows, destination countries, and privacy, legal, and copyright documentation to support GDPR, NIS2, and DORA assessments. Delivers real-time in-app notifications when scans complete, fail, or are cancelled. Adds redesigned EASM interface with improved navigation, with the previous interface still accessible as Legacy UI . Introduces multi-project visibility, scan scheduling, and AI-powered intelligence for centralized risk management and scan orchestration.
+3 more
show less
Adds a Findings view with improved prioritization workflows and expanded reporting capabilities. Adds an Issues capability to streamline remediation efforts and improve focus on cyber hygiene. Enables exporting web applications from EASM directly into DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Validates components against the EASM knowledge base so risk scores reflect real vulnerabilities per version, not just software age.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Collects compliance evidence for cookie consent tracking, third-party data flows, destination countries, and privacy, legal, and copyright documentation to support GDPR, NIS2, and DORA assessments. Delivers real-time in-app notifications when scans complete, fail, or are cancelled. Introduces multi-project visibility, scan scheduling, and AI-powered intelligence for centralized risk management and scan orchestration. Adds a Findings view with improved prioritization workflows and expanded reporting capabilities.
+2 more
show less
Adds an Issues capability to streamline remediation efforts and improve focus on cyber hygiene. Enables exporting web applications from EASM directly into DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
1 more in Everything
CLI updates (2026-10-23)
Oct 23, 2026
·
issue 119
Veracode CLI gains veracode scan static, veracode findings static, async fix mode, --csharp-source, --skip-packagers, and more across recent releases.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Run a static scan on your Git repo and immediately review findings without leaving the command line.
copy
$ veracode scan static Package a C# project's source code directly for Static Analysis in a CI pipeline without a build step.
copy
$ veracode package --csharp-source
Adds veracode scan static command to run static scans and review security findings within a Git workflow.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds veracode findings static command to access cached static scan findings in the local Veracode directory. Adds --csharp-source flag to veracode package to package C# source code directly for Static Analysis without compiling it into binaries. Adds --skip-packagers flag to veracode package to exclude specific artifacts (e.g. unsupported SQL) from packaging without affecting other languages. Adds --java-source flag and VERACODE_PACKAGE_JAVA_SOURCE=true environment variable to veracode package to support Java source code packaging.
+5 more
show less
Adds VERACODE_PACKAGE_GOLANG_GENERATE environment variable to veracode package to enable client-side CGO code generation when packaging Go applications. Adds SRCLR_MAKE_WINDOWS environment variable to support preprocessing C/C++ source files with Make on Windows using a native Windows gcc or clang compiler. Adds --exclude flag to veracode package to prevent specified Java packages or JAR files from being scanned. Adds veracode fix sca command to generate fixes for vulnerable dependencies identified in SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. Adds async Fire-and-Forget (FnF) mode to veracode fix sca, submitting remediation requests for background processing without waiting for fixes or pull requests.
Adds veracode scan static command to run static scans and review security findings within a Git workflow.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds veracode findings static command to access cached static scan findings in the local Veracode directory. Adds veracode fix sca command to generate fixes for vulnerable dependencies identified in SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
7 more in Everything
Fix updates (2026-10-22)
Oct 22, 2026
·
issue 117
Veracode Fix for SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. veracode fix sca CLI command for dependency remediation.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Trigger SCA-based dependency fix suggestions from the CLI against a project with vulnerable dependencies.
Adds veracode fix sca CLI command (and SCM SCM Source Code Management: version-control systems (Git, SVN, etc.) that track changes to code over time, giving cyber tools reproducible builds, audit trails, and collaborative development workflows. Veracode Fix for SCA now processes fix requests from the GitHub Workflow Integration asynchronously, freeing the GitHub Actions GitHub Actions GitHub's built-in CI/CD system that runs automated workflows triggered by repository events, letting cyber tools automate testing, building, and releasing without managing separate pipeline infrastructure.
Adds veracode fix sca CLI command (and SCM SCM Source Code Management: version-control systems (Git, SVN, etc.) that track changes to code over time, giving cyber tools reproducible builds, audit trails, and collaborative development workflows.
1 more in Everything
Veracode CLI v2.53.0 adds veracode scan static and veracode findings static commands plus a --csharp-source flag for source-based C# scanning.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds --csharp-source flag to the Veracode CLI to package C# source code directly for Static Analysis without compiling it into binaries.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds veracode scan static command to run static scans and review security findings within a Git workflow. Adds veracode findings static command to access cached static scan findings in the local Veracode directory. Adds build_runs_on support for SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. Automatically includes .properties files when packaging Java source code in Veracode CLI v2.53.0.
+1 more
show less
EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do.
Adds --csharp-source flag to the Veracode CLI to package C# source code directly for Static Analysis without compiling it into binaries.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds veracode scan static command to run static scans and review security findings within a Git workflow. Adds veracode findings static command to access cached static scan findings in the local Veracode directory.
3 more in Everything
CLI updates (2026-10-13)
Oct 13, 2026
·
issue 111
Veracode CLI v2.53.0 adds veracode scan static and veracode findings static commands plus --csharp-source flag for C# source packaging.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
Run a static scan within your Git workflow and then retrieve cached findings from the local Veracode directory for fast CI feedback without re-scanning.
copy
$ veracode scan static && veracode findings static Generate SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds new packaging support to veracode package: the --csharp-source flag to package C# source code directly for Static Analysis without compiling it into binaries, and generic packager support for Apex.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Introduces the veracode scan static command to run static scans and review security findings within a Git workflow, and the veracode findings static command to access cached static scan findings in the local Veracode directory. Adds multiple packaging improvements to veracode package: the --skip-packagers flag to exclude specific artifacts (e.g. unsupported SQL) from packaging without affecting other languages; support for requirements-dev.txt in Python packaging workflows; exit codes 5, 6, and 7 to improve CI/CD automation and error handling; the --exclude flag to prevent specified Java packages or JAR files from being scanned; the VERACODE_PACKAGE_JAVA_SOURCE=true environment variable and --java-source flag for Java source code packaging; the VERACODE_PACKAGE_GOLANG_GENERATE environment variable to enable client-side CGO code generation for Go applications; the SRCLR_MAKE_WINDOWS environment variable to enable preprocessing C/C++ source files with Make on Windows using a native Windows gcc or clang compiler; automatic inclusion of .yaml, .yml, and .properties files when packaging Java source code; support for the Poetry package management tool for Python autopackaging; support for the MSBuild .NET framework; and support for Go v1.24. Supports the veracode dynamic scan command with target UUIDs UUIDs A universally unique identifier, usually a 128-bit value used to identify an object across systems. It is designed to make independently generated identifiers unlikely to collide. Introduces the veracode package discover command to detect toolchains required to create scannable artifacts.
+5 more
show less
Introduces the veracode fix sca command (Limited Availability) to generate fixes for vulnerable dependencies identified in SCA scans. Adds veracode sca SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. CycloneDX 1.6 CycloneDX 1.6 An OWASP-maintained Software Bill of Materials standard that catalogs components, dependencies, and supply-chain metadata; tools use it to produce or consume machine-readable SBOMs in a widely supported schema. SPDX 2.3 SPDX 2.3 An open standard from the Linux Foundation for describing software bills of materials, letting cyber tools exchange dependency, license, and vulnerability data in a common machine-readable format. Introduces auth login command to onboard new users via oAuth2. Enhances the veracode package discover command with toolchain detection for JavaScript projects using npm or Yarn, toolchain detection for Java projects using the Gradle package manager, and new exit codes. Enhances the veracode scan command by allowing a custom policy defined in the Veracode Platform to be applied and viewing policy evaluation for individual findings alongside the overall policy result, enabling specification of a custom location from which vulnerability databases can be downloaded, adding support for parsing Dockerfile heredoc syntaxes, categorizing secret-type findings as Critical in scan results, and prioritizing vulnerability results from the NVD NVD The National Vulnerability Database, maintained by NIST, is the U.S. government repository of CVE records enriched with CVSS scores and metadata; cyber tools query it to drive vulnerability prioritization.
Adds new packaging support to veracode package: the --csharp-source flag to package C# source code directly for Static Analysis without compiling it into binaries, and generic packager support for Apex.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Introduces the veracode scan static command to run static scans and review security findings within a Git workflow, and the veracode findings static command to access cached static scan findings in the local Veracode directory. Introduces the veracode package discover command to detect toolchains required to create scannable artifacts. Introduces the veracode fix sca command (Limited Availability) to generate fixes for vulnerable dependencies identified in SCA scans. Introduces auth login command to onboard new users via oAuth2.
5 more in Everything
└──▷ BREAKING ON UPGRADE
! The SRCCLR_DOWNLOAD_URL environment variable default is now https://sca-downloads.veracode.com; the previous URL https://download.sourceclear.com is deprecated and all instances should be updated.
Integration updates (2026-10-13)
Oct 13, 2026
·
issue 108
Veracode integrations gain new predependency_command, policy, and build_runs_on params across GitHub, GitLab, and Azure DevOps workflow configs︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ USE IT
Run a build script before Veracode packages your project in a GitHub static scan pipeline.
veracode.yml
copy
predependency_command: mvn package -DskipTests
Enforce an IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup.
veracode.yml
copy
policy: My IaC Policy
Pin scheduled Azure DevOps workflow scans to a specific analysis branch instead of the repo default.
veracode.yml
copy
analysis_branch: release/2026-q4
Adds new veracode.yml parameters across Workflow Integrations: predependency_command for GitHub Workflow Integration v2.1.9, GitLab Workflow Integration v2.1.9, and Azure DevOps Workflow Integration v2.4.4, enabling single-line or multiline commands to run before Veracode packages the project; build_runs_on for GitHub Workflow Integration v2.1.9 SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. policy for Azure DevOps Workflow Integration v2.4.5, GitLab Workflow Integration v2.1.9, and GitHub Workflow Integration v2.1.7 infrastructure-as-code (IaC) scans; and support for a custom agent pool name parameter for Azure DevOps Workflow Integration v2.4.3, letting you specify the agent pool for pipeline execution.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds analysis_branch support in veracode.yml for Azure DevOps Workflow Integration v2.3.10 so scheduled scans run against the specified branch instead of the default branch. Adds a Scan Scope setting to Veracode Scan for Visual Studio v0.8.0 to scan the full project directory or only the active solution for faster, more focused results. Adds a Current File filter and an option to filter and group Static Scan Findings by file name, with findings for each file grouped by severity, to Static Scan Findings in Veracode Scan for VS Code v1.16.3. Adds an option to change the region during OAuth authentication in Veracode Scan for VS Code v1.16.3, displaying the current or most recently used region below Authentication .
+5 more
show less
Adds a Mitigated Findings section to the Flaws That Violate Policy view in Veracode Scan for VS Code v1.16.4 for findings with approved mitigations. Adds a new uninstallation workflow on the Veracode Platform for removing the Veracode app from GitHub organizations (GitHub Workflow Integration v2.1.1). Enables installing, configuring, and updating the Veracode GitHub Integration directly from the Veracode Platform (eliminating manual GitHub Marketplace steps), and enables scheduling Static Analysis, SCA, and IaC scans for GitHub organizations directly from the Veracode Platform (GitHub Workflow Integration v2.0.0). Adds autopackaging support for Apex, VB6, and Perl in GitHub Workflow Integration v2.0.0. Adds support for Jira 11 in Veracode Integration for Jira Server v5.0.2, including required Java 21 and platform compatibility updates.
Adds new veracode.yml parameters across Workflow Integrations: predependency_command for GitHub Workflow Integration v2.1.9, GitLab Workflow Integration v2.1.9, and Azure DevOps Workflow Integration v2.4.4, enabling single-line or multiline commands to run before Veracode packages the project; build_runs_on for GitHub Workflow Integration v2.1.9 SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. policy for Azure DevOps Workflow Integration v2.4.5, GitLab Workflow Integration v2.1.9, and GitHub Workflow Integration v2.1.7 infrastructure-as-code (IaC) scans; and support for a custom agent pool name parameter for Azure DevOps Workflow Integration v2.4.3, letting you specify the agent pool for pipeline execution.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds a Scan Scope setting to Veracode Scan for Visual Studio v0.8.0 to scan the full project directory or only the active solution for faster, more focused results. Adds a Current File filter and an option to filter and group Static Scan Findings by file name, with findings for each file grouped by severity, to Static Scan Findings in Veracode Scan for VS Code v1.16.3. Adds a Mitigated Findings section to the Flaws That Violate Policy view in Veracode Scan for VS Code v1.16.4 for findings with approved mitigations. Adds a new uninstallation workflow on the Veracode Platform for removing the Veracode app from GitHub organizations (GitHub Workflow Integration v2.1.1).
+1 more
show less
Enables installing, configuring, and updating the Veracode GitHub Integration directly from the Veracode Platform (eliminating manual GitHub Marketplace steps), and enables scheduling Static Analysis, SCA, and IaC scans for GitHub organizations directly from the Veracode Platform (GitHub Workflow Integration v2.0.0).
4 more in Everything
└──▷ BREAKING ON UPGRADE
! Veracode Azure DevOps Extension v4.0.0 requires manual migration of existing pipelines from v3 to v4 for both Azure DevOps Server and Azure DevOps (Cloud); the deprecated Veracode Flaw Importer v3 task is replaced by VeracodeFlawImporter v4.! Veracode will end support for the Veracode Integration for Jira on Jira Server and Jira Data Center 9.x on November 30, 2026; upgrade to Jira 10 or later to continue using a supported version.
SCA updates (2026-10-12)
Oct 12, 2026
·
issue 107
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. --appname and --show-cli flags, malicious package detection, Poetry Poetry A Python dependency manager and packaging tool that handles virtual environments, version pinning, and publishing in one workflow, replacing the older pip-plus-setuptools approach. SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue.
└──▷ TRY IT
Link an SCA agent scan to a named application profile for centralized visibility in the Veracode Platform.
copy
$ srcclr scan . --appname 'MyApp' --json --show-cli Save structured JSON scan output to a file while keeping a human-readable summary visible in CI console logs.
copy
$ srcclr scan . --json results.json --show-cli
Adds --appname and --show-cli flags to the SCA agent scan command: --appname (Commercial region) links scan results to an application profile and requires OAuth or HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it. --show-cli, used with --json, saves JSON output to a file while still displaying a human-readable CLI summary in the console, returning an error if used without --json.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds malicious package detection to SCA upload and agent-based scans, reporting malicious packages found in scanned libraries with no extra configuration or agent update required. Adds SBOM support to SCA scans: SBOM generation during SCA agent-based scans and SBOM file scanning support as part of SCA upload scans. Adds support for Python projects using the Poetry package manager to both SCA agent-based scans and SCA Upload scans. Adds Python 3.12 environment support for SCA agent-based scans.
+3 more
show less
Adds Unified Policy assignment to SCA agent-based scan workspaces in the US Federal region and the European region, allowing policies to create issues and break builds based on defined criteria. Changes default Veracode URLs for SCA: the Platform backend API URL for Commercial region scans moves to https://sca-api.veracode.com (from https://api.sourceclear.io), the European region API URL moves to https://sca-api.veracode.eu and the US Federal region API URL moves to https://sca-api.veracode.us (replacing platform-backend.analysiscenter.veracode.eu and platform-backend.analysiscenter.veracode.us), and the SCA agent download URL moves to https://sca-downloads.veracode.com (from https://download.sourceclear.com); all legacy URLs remain available for 12 months. Adds deep-link support for SCA pages: unauthenticated users opening a scan-results link are redirected to login and then back to the original page.
Adds --appname and --show-cli flags to the SCA agent scan command: --appname (Commercial region) links scan results to an application profile and requires OAuth or HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it. --show-cli, used with --json, saves JSON output to a file while still displaying a human-readable CLI summary in the console, returning an error if used without --json.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds malicious package detection to SCA upload and agent-based scans, reporting malicious packages found in scanned libraries with no extra configuration or agent update required. Adds SBOM support to SCA scans: SBOM generation during SCA agent-based scans and SBOM file scanning support as part of SCA upload scans. Adds deep-link support for SCA pages: unauthenticated users opening a scan-results link are redirected to login and then back to the original page.
4 more in Everything
└──▷ BREAKING ON UPGRADE
! The default SCA agent download URL changes from https://download.sourceclear.com to https://sca-downloads.veracode.com; scripts or pipelines that hardcode the old URL must be updated within 12 months before https://download.sourceclear.com is retired.! The default Veracode Platform backend API URL for Commercial region SCA agent scans changes from https://api.sourceclear.io to https://sca-api.veracode.com; any configuration referencing the legacy SourceClear URL must be updated within 12 months.! The default Veracode Platform backend API URLs for European region customers change from https://platform-backend.analysiscenter.veracode.eu to https://sca-api.veracode.eu, and for US Federal region customers from https://platform-backend.analysiscenter.veracode.us to https://sca-api.veracode.us; legacy URLs retire in 12 months.
Integration updates (2026-10-09)
Oct 9, 2026
·
issue 100
Veracode integrations gain IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
└──▷ USE IT
Run a pre-packaging setup script before Veracode scans your project in a GitLab or Azure DevOps pipeline.
veracode.yml
copy
# veracode.yml
predependency_command: pip install -r requirements.txt
Apply an IaC policy check as part of a GitHub, GitLab, or Azure DevOps workflow scan.
veracode.yml
copy
# veracode.yml
policy: 'Veracode Recommended Medium'
Restrict scheduled Azure DevOps scans to a specific analysis branch rather than the default branch.
veracode.yml
copy
# veracode.yml
analysis_branch: main-security
Java API wrapper v26.10.20.1 changes Git metadata collection so the repository URL in the Veracode application profile is updated only when -repourl is explicitly specified.
1 more in Everything
└──▷ BREAKING ON UPGRADE
! Veracode Azure DevOps Extension v4.0.0 requires manually migrating existing pipelines from v3 to v4 for both Azure DevOps Server and Azure DevOps (Cloud); the deprecated Veracode Flaw Importer v3 task is replaced by VeracodeFlawImporter v4.! Veracode will end support for the Veracode Integration for Jira on Jira Server and Jira Data Center 9.x on November 30, 2026; upgrade to Jira 10 or later to continue using a supported version.
Integration updates (2026-10-08)
Oct 8, 2026
·
issue 098
Veracode integrations add IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup.
Adds policy parameter to veracode.yml in the Azure DevOps, GitLab, and GitHub Workflow Integrations for infrastructure-as-code (IaC) scans. Adds predependency_command parameter to veracode.yml in the GitLab and Azure DevOps Workflow Integrations to run commands before Veracode packages the project. Java API wrapper v26.10.20.0 automatically includes Git repository and commit metadata (branch, commit, author, repository, and Git provider) in Static Analysis scans for JAR, WAR, EAR, and ZIP archives. New integration GitHub Workflow Integration v2.0.0 enables installing, configuring, and scheduling Static Analysis, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. GitHub Workflow Integration adds a new uninstallation workflow on the Veracode Platform.
+3 more
show less
Adds a Mitigated Findings section to the Flaws That Violate Policy view, a Current File filter, and file-name grouping to Static Scan Findings in Veracode Scan for VS Code. Veracode Scan for Visual Studio v0.8.0 adds a Scan Scope setting to scan the full project directory or only the active solution. Veracode Azure DevOps Extension v4.0.0 replaces Veracode Flaw Importer v3 with VeracodeFlawImporter v4; existing pipelines must be manually migrated from v3 to v4.
8 details in Everything
└──▷ BREAKING ON UPGRADE
! Veracode Azure DevOps Extension v4.0.0 deprecates Veracode Flaw Importer v3 and replaces it with VeracodeFlawImporter v4; existing pipelines must be manually migrated from v3 to v4.
Veracode adds predependency_command for Azure DevOps pipelines and team-availability controls in Security Labs.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ USE IT
Run a dependency install or environment setup script before Veracode packages your project in an Azure DevOps pipeline.
yaml
copy
predependency_command: |
  pip install -r requirements.txt
  export BUILD_ENV=production
└──▷ BREAKING ON UPGRADE
! Existing Azure DevOps pipelines using the v3 tasks (VeracodeFlawImporter v3, Upload and Scan v3) must be manually migrated to v4; Azure DevOps Server users should upgrade from v3.35.0 to v4.0.0 without uninstalling the previous version first.
Veracode adds team filtering for large orgs, a new predependency_command param, and VS Code mitigated-findings view.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds predependency_command parameter to Azure DevOps Workflow Integration v2.4.4, letting pipelines run single-line or multiline commands before Veracode packages the project.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds a Mitigated Findings section to the Flaws That Violate Policy view in Veracode Scan for VS Code v1.16.4, surfacing findings with approved mitigations. Enables organizations with more than 500 teams to select which teams are available for use in Security Labs. Replaces Veracode Flaw Importer v3 with VeracodeFlawImporter v4 and updates Upload and Scan to v4 in the Azure DevOps Extension v4.0.0.
Adds predependency_command parameter to Azure DevOps Workflow Integration v2.4.4, letting pipelines run single-line or multiline commands before Veracode packages the project.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
3 more in Everything
└──▷ BREAKING ON UPGRADE
! Azure DevOps Extension v4.0.0 deprecates Flaw Importer v3 and requires manually migrating existing pipelines from v3 to v4 for both Azure DevOps Server and Azure DevOps (Cloud).
Integration updates (2026-09-30)
Sep 30, 2026
·
issue 090
Veracode: Adds the policy parameter to veracode.yml for infrastructure-as-code (IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup.
└──▷ USE IT
Run a build-tool installation script before Veracode packages your project in an Azure DevOps pipeline.
veracode.yml
copy
predependency_command: pip install -r requirements.txt
Target a specific analysis branch for scheduled Azure DevOps scans instead of the repository default branch.
veracode.yml
copy
analysis_branch: release/2.0
predependency_command: mvn clean package -DskipTests
Adds support for the predependency_command parameter in veracode.yml for Azure DevOps Workflow Integration v2.4.4, enabling single-line or multiline commands to run before Veracode packages the project. Adds support for Jira 11 (including Java 21 and platform compatibility) in Veracode Integration for Jira Server v5.0.2. Replaces Veracode Flaw Importer v3 with VeracodeFlawImporter v4 and updates Upload and Scan to v4 in Veracode Azure DevOps Extension v4.0.0.
Adds support for the predependency_command parameter in veracode.yml for Azure DevOps Workflow Integration v2.4.4, enabling single-line or multiline commands to run before Veracode packages the project.
2 more in Everything
└──▷ BREAKING ON UPGRADE
! Veracode Azure DevOps Extension v4.0.0 deprecates Veracode Flaw Importer v3 and replaces it with VeracodeFlawImporter v4; existing pipelines must be manually migrated from v3 to v4 (Azure DevOps Server must upgrade from v3.35.0 to v4.0.0 without uninstalling the previous version).! On November 30, 2026, Veracode will end support for the Veracode Integration for Jira on Jira Server and Jira Data Center 9.x; users must upgrade to Jira 10 or later to remain on a supported version.! The GitHub Veracode Workflow App no longer has administration permissions, meaning it can no longer alter or remove repositories where it is installed.
Veracode Azure DevOps Extension v4.0.0
Sep 30, 2026
· release notes
Veracode Azure DevOps Extension v4.0.0 replaces Flaw Importer v3 with v4 and updates Upload/Scan components
Replaces VeracodeFlawImporter v3 task with the new VeracodeFlawImporter v4 task for importing flaws into Azure DevOps pipelines. Updates the existing Upload and Scan tasks to their latest versions within the extension.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! The VeracodeFlawImporter v3 task is deprecated; pipelines must be manually migrated to use VeracodeFlawImporter v4 or higher.! Existing Azure DevOps pipelines must be manually migrated from v3 to v4 to utilize the updated Upload and Scan tasks.
Training updates (2026-09-29)
Sep 29, 2026
·
issue 089
Veracode Security Labs gains team selection for large orgs, Veracode Platform IAM IAM Identity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access.
Adds updatedAfter parameter to the Get Lesson Progress API to support incremental loads.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds excludeNotStarted=true parameter to the Get Lesson Progress API to filter out lessons that have not been started. Adds stack field and updated_on field to the Get Lesson Progress API response; shows Not Started when both start_time and end_time are null. Enables organizations with more than 500 teams to select which teams are available for use in Security Labs. Integrates Security Labs users and teams management with the Veracode Platform, authenticating Security Labs users through Veracode IAM (Identity and Access Management).
+10 more
show less
Allows Security Labs administrators and managers to search teams within Security Labs. Adds in-app guidance for creating campaigns and using reporting in Security Labs. Adds new OWASP Top 10:2025 OWASP Top 10:2025 A ranked list of the ten most critical web application risk categories, maintained by the Open Worldwide Application Security Project, used by cyber tools to prioritize detection, testing, and remediation coverage. Adds new OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code. Adds Container Security in Docker Security Labs lessons covering Users, Virtualization, Networking, Resources, Inventory, and Orchestration topics. Adds six new eLearning secure coding courses aligned to OWASP Top 10:2025 for .NET, Java, JavaScript, PHP, Python, and Security Awareness, available with English, Spanish, French, Portuguese, and Chinese captions. Adds CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. CWEs CWEs A community-maintained list of software and hardware weakness types, maintained by MITRE, that gives cyber tools a standard taxonomy for classifying and communicating vulnerability root causes. Adds code syntax highlighting in Security Labs lessons tailored to programming languages. Extends eLearning report date range selection to up to one year in the past. Adds assessment quiz eLearning courses for User and application setup, Static Analysis, Dynamic Analysis, Scan and fix in your IDE, and SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds updatedAfter parameter to the Get Lesson Progress API to support incremental loads.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enables organizations with more than 500 teams to select which teams are available for use in Security Labs. Integrates Security Labs users and teams management with the Veracode Platform, authenticating Security Labs users through Veracode IAM (Identity and Access Management). Allows Security Labs administrators and managers to search teams within Security Labs. Adds in-app guidance for creating campaigns and using reporting in Security Labs.
+7 more
show less
Adds new OWASP Top 10:2025 OWASP Top 10:2025 A ranked list of the ten most critical web application risk categories, maintained by the Open Worldwide Application Security Project, used by cyber tools to prioritize detection, testing, and remediation coverage. Adds new OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code. Adds Container Security in Docker Security Labs lessons covering Users, Virtualization, Networking, Resources, Inventory, and Orchestration topics. Adds six new eLearning secure coding courses aligned to OWASP Top 10:2025 for .NET, Java, JavaScript, PHP, Python, and Security Awareness, available with English, Spanish, French, Portuguese, and Chinese captions. Adds CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. CWEs CWEs A community-maintained list of software and hardware weakness types, maintained by MITRE, that gives cyber tools a standard taxonomy for classifying and communicating vulnerability root causes. Adds code syntax highlighting in Security Labs lessons tailored to programming languages. Adds assessment quiz eLearning courses for User and application setup, Static Analysis, Dynamic Analysis, Scan and fix in your IDE, and SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
3 more in Everything
└──▷ BREAKING ON UPGRADE
! The default Security Labs URL has changed from https://securitylabs.veracode.com/ to https://securitylabs.veracode.com/security-labs/; customers using SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. ! In Security Labs, Teams are now called Organizations and Roles are now called Teams ; any documentation or automation referencing the old terminology must be updated.! The Veracode eLearning REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. ! 33 deprecated eLearning courses (OWASP 2017, OWASP Top 10 (2021), Secure Coding for .NET, Java, JavaScript, PHP, Python — 6 courses each, Python 3 courses) are no longer available; certification levels have been updated to include newer replacement courses.! The OWASP Top 10 (2021) Security Labs lessons are no longer available.! The Security Labs community edition is deprecated as of July 31, 2026.
Integration updates (2026-09-28)
Sep 28, 2026
·
issue 088
Veracode integrations gain IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
└──▷ USE IT
Enforce a named policy on IaC scans in your GitHub workflow so failures are gated against your organisation's policy, not just the default.
veracode.yml
copy
# veracode.yml
iac:
  policy: 'PCI-DSS Strict'
Adds support for custom predependency commands in the Veracode YAML file to prepare projects before scanning in GitHub Workflow Integration v2.1.3. Adds a custom agent pool name parameter to veracode.yml in Azure DevOps Workflow Integration v2.4.3 to specify the agent pool for pipeline execution. Adds support for scheduling analysis_branch scans in Azure DevOps Workflow Integration v2.3.10, so scheduled scans run against the specified branch instead of the default branch when analysis_branch is set in veracode.yml. Enables scheduling of scans for every organization where the Azure DevOps Workflow Integration is installed, driven by veracode.yml configuration. Adds a Current File filter to Static Scan Findings in Veracode Scan for VS Code v1.16.3, allowing findings to be scoped to the file open in the editor.
+13 more
show less
Adds an option to filter and group Static Scan Findings by file name in Veracode Scan for VS Code v1.16.3, with findings grouped by severity per file. Adds an option to change the region during OAuth authentication in Veracode Scan for VS Code v1.16.3, displaying the current or most recently used region below the Authentication screen. Adds a Mitigated Findings section to the Flaws That Violate Policy view in Veracode Scan for VS Code v1.16.4 for findings with approved mitigations. Enables installation, configuration, and credential updates for the GitHub Workflow Integration directly from the Veracode Platform, eliminating GitHub Marketplace manual steps. Adds a new uninstallation workflow for the Veracode app from GitHub organizations via the Veracode Platform. Adds autopackaging support for Apex, VB6, and Perl in GitHub Workflow Integration v2.0.0. Enables scheduling of Static Analysis, SCA, and IaC scans from the Veracode Platform for GitHub organizations where the integration is installed. Adds a Scan Scope setting in Veracode Scan for Visual Studio v0.8.0 to scan either the full project directory or only the active solution. Adds usage analytics to Veracode Scan for JetBrains v1.8.0 to provide insights into plugin adoption, feature usage, and scan activity. Adds usage analytics to Veracode Scan for VS Code v1.16.0 to provide insights into plugin adoption, feature usage, and scan activity. Adds usage analytics to Veracode Scan for Visual Studio v0.8.0 to provide insights into plugin adoption, feature usage, and scan activity. Adds page size support to the Platform Applications API (/appsec/v1/applications) in Java API Wrapper v26.3.19.0 to improve efficiency when retrieving large application lists. Introduces support for the Veracode Platform paginated Sandbox REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Adds support for custom predependency commands in the Veracode YAML file to prepare projects before scanning in GitHub Workflow Integration v2.1.3. Adds a custom agent pool name parameter to veracode.yml in Azure DevOps Workflow Integration v2.4.3 to specify the agent pool for pipeline execution. Enables scheduling of scans for every organization where the Azure DevOps Workflow Integration is installed, driven by veracode.yml configuration. Adds a Current File filter to Static Scan Findings in Veracode Scan for VS Code v1.16.3, allowing findings to be scoped to the file open in the editor. Adds an option to filter and group Static Scan Findings by file name in Veracode Scan for VS Code v1.16.3, with findings grouped by severity per file.
+11 more
show less
Adds an option to change the region during OAuth authentication in Veracode Scan for VS Code v1.16.3, displaying the current or most recently used region below the Authentication screen. Adds a Mitigated Findings section to the Flaws That Violate Policy view in Veracode Scan for VS Code v1.16.4 for findings with approved mitigations. Enables installation, configuration, and credential updates for the GitHub Workflow Integration directly from the Veracode Platform, eliminating GitHub Marketplace manual steps. Adds a new uninstallation workflow for the Veracode app from GitHub organizations via the Veracode Platform. Adds autopackaging support for Apex, VB6, and Perl in GitHub Workflow Integration v2.0.0. Enables scheduling of Static Analysis, SCA, and IaC scans from the Veracode Platform for GitHub organizations where the integration is installed. Adds a Scan Scope setting in Veracode Scan for Visual Studio v0.8.0 to scan either the full project directory or only the active solution. Adds usage analytics to Veracode Scan for JetBrains v1.8.0 to provide insights into plugin adoption, feature usage, and scan activity. Adds usage analytics to Veracode Scan for VS Code v1.16.0 to provide insights into plugin adoption, feature usage, and scan activity. Adds usage analytics to Veracode Scan for Visual Studio v0.8.0 to provide insights into plugin adoption, feature usage, and scan activity. Introduces support for the Veracode Platform paginated Sandbox REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
2 more in Everything
Veracode Scan for VS Code v1.16.4 adds a Mitigated Findings section to the Flaws That Violate Policy view.
└──▷ HOW TO FIND IT
Review findings that have been explicitly mitigiated but still violate policy within the VS Code interface.
📍 In VS Code, open the Veracode Scan view and navigate to Flaws That Violate Policy to see the new Mitigated Findings section.
Veracode Scan for VS Code v1.16.4 adds Mitigated Findings section to Flaws That Violate Policy view
Veracode adds multi-team DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
└──▷ HOW TO FIND IT
Assign two teams to a DAST web application target so both AppSec AppSec Application security: the practice of finding and fixing vulnerabilities in software during design, development, and testing. Cyber tools build on AppSec workflows to shift vulnerability detection earlier in the development lifecycle.
📍 In the Veracode Platform, go to DAST › Targets › Create Web Application. Under Teams , select multiple teams from the dropdown (e.g., AppSec and DevOps ), then save the target.
Adds the policy parameter to the GitHub Workflow Integration v2.1.7 for infrastructure-as-code (IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Enables assigning multiple teams to a DAST target when creating a web application or API specification. Integrates Veracode Static Analysis with DryRun Security, surfacing Veracode findings and remediation guidance inside pull request and code review workflows. Makes the IDE and CLI Usage Explore and Dashboard available in the European Region. Adds support for Jira 11 (including Java 21 compatibility) in Veracode Integration for Jira Server v5.0.2.
Adds the policy parameter to the GitHub Workflow Integration v2.1.7 for infrastructure-as-code (IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Integrates Veracode Static Analysis with DryRun Security, surfacing Veracode findings and remediation guidance inside pull request and code review workflows.
3 more in Everything
Veracode: Adds support for Jira 11 (including Java 21 and platform compatibility) in Veracode Integration for Jira Server v5.0.2.
Veracode: Adds support for iOS 27 in the Static Analysis Engine v2026.09.
Adds support for Go 1.27 in the Static Analysis Engine v2026.09. Redesigns the EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do. Improves detection of CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. Improves detection of CWE-89 flaws in PySpark applications and improves SQLAlchemy analysis to reduce CWE-89 false positives in the Static Analysis Engine v2026.09. Improves detection of CWE-200 flaws in the Static Analysis Engine v2026.09, reducing false positives.
+1 more
show less
Improves analysis of CALL commands to enhance detection of CWE-252 flaws in the Static Analysis Engine v2026.09.
6 more in Everything
Platform updates (2026-09-24)
Sep 24, 2026
·
issue 086
Veracode adds Custom PDF REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. XML APIs XML APIs Interfaces for reading, writing, or querying XML documents, provided by libraries such as libxml2 or built into language runtimes; cyber tools use them to parse structured data like configs, reports, or protocol messages reliably.
Adds a Custom PDF REST API to programmatically generate custom PDF reports.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds OAuth Client Credentials authentication support for Veracode XML APIs, in addition to the existing REST API support. Adds most_recent_scan filter to the Reporting API Scans report; when set to true, returns only the most recent scan per asset. Adds custom_severity filter to the Reporting API Findings report. Adds collections_list field to the Finding Reporting API response, returning a list of collection names associated with the application.
+17 more
show less
Adds library_instance_ref field to the Veracode Reporting API findings response to uniquely identify the specific library instance associated with a finding. Adds data_refresh_date field to the Reporting API to indicate the most recent Analytics data refresh time. Adds action_type filter to the Audit Log report in the Reporting REST API for retrieving audit log records based on specific user actions. Adds an Audit Log report to the Reporting REST API to query Veracode Analytics for detailed user activity information. Introduces the IDE and CLI Usage Explore and Dashboard in Veracode Analytics to visualize your organization's IDE and CLI plugin usage. Adds a Firewall Usage Dashboard and Firewall Usage Explore in Veracode Analytics for metrics on Veracode Firewall. Adds Collections fields to the Applications explore in Veracode Analytics, and new Collections visualizations to the Policy Compliance Overview dashboard. Adds support for creating and managing OAuth 2.0 OAuth 2.0 An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms. Adds Manual Penetration Testing (MPT) Flaw Matching to correlate findings across tests, providing consistent flaw IDs, status values, and inclusion in remediation grace periods. Adds container and IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Enables mapping multiple domains to a single identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. SP-initiated SP-initiated A SAML or OAuth/OIDC login flow where the Service Provider redirects the user to an Identity Provider to authenticate, rather than the IdP pushing an assertion unprompted; tools use it to trigger SSO from their own login page. SAML SSO SAML SSO An authentication protocol that lets a user log in once with an identity provider and access multiple services without re-entering credentials, by passing signed XML assertions between parties. Allows disabling Veracode-defined roles for users who use custom roles, via the Identity API. Updates the Auto-Update OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. OWASP Top 10:2025 OWASP Top 10:2025 A ranked list of the ten most critical web application risk categories, maintained by the Open Worldwide Application Security Project, used by cyber tools to prioritize detection, testing, and remediation coverage. MITRE MITRE A US federally funded research and development center that maintains public frameworks—ATT&CK, CVE, D3FEND—that cyber tools use to classify threats, vulnerabilities, and defensive techniques in a common language. Adds six new built-in security policies to the Veracode Platform. Upgrades Veracode Analytics to Looker 26.6, adding finer widget size granularity, persistent filtering, and tabbed dashboards. Customizable PDF now includes SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. Reduces Veracode Analytics data refresh time from four hours to two hours.
Adds a Custom PDF REST API to programmatically generate custom PDF reports.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds OAuth Client Credentials authentication support for Veracode XML APIs, in addition to the existing REST API support. Adds an Audit Log report to the Reporting REST API to query Veracode Analytics for detailed user activity information. Introduces the IDE and CLI Usage Explore and Dashboard in Veracode Analytics to visualize your organization's IDE and CLI plugin usage. Adds a Firewall Usage Dashboard and Firewall Usage Explore in Veracode Analytics for metrics on Veracode Firewall.
+5 more
show less
Adds support for creating and managing OAuth 2.0 OAuth 2.0 An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms. Adds Manual Penetration Testing (MPT) Flaw Matching to correlate findings across tests, providing consistent flaw IDs, status values, and inclusion in remediation grace periods. Adds container and IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Enables mapping multiple domains to a single identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. SP-initiated SP-initiated A SAML or OAuth/OIDC login flow where the Service Provider redirects the user to an Identity Provider to authenticate, rather than the IdP pushing an assertion unprompted; tools use it to trigger SSO from their own login page. SAML SSO SAML SSO An authentication protocol that lets a user log in once with an identity provider and access multiple services without re-entering credentials, by passing signed XML assertions between parties. Adds six new built-in security policies to the Veracode Platform.
12 more in Everything
└──▷ BREAKING ON UPGRADE
! The Veracode Healthcheck endpoint /healthcheck/status has been removed and now returns 404; use the v2/principal endpoint in the Identity REST API instead.
The IDE and CLI Usage Explore and Dashboard are now available in the European Re
Sep 24, 2026
· release notes
Veracode expands geographic reach for IDE and CLI analytics.
IDE and CLI Usage Explore dashboard now serves data from the European Region.
1 detail in Everything
Veracode adds DryRun Security integration, IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do.
Adds the policy parameter to GitHub Workflow Integration v2.1.7 for infrastructure-as-code (IaC) scans.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Integrates Veracode Static Analysis with DryRun Security, surfacing Veracode findings and remediation guidance inside pull request and code review workflows.
2 details in Everything
CLI updates (2026-09-23)
Sep 23, 2026
·
issue 086
Veracode CLI gains SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue.
└──▷ TRY IT
Generate SCA-based dependency fixes for a JavaScript project after running an SCA scan.
Package a Java project excluding a specific JAR that causes false positives or is unsupported.
copy
$ veracode package --exclude com.example:legacy-lib ./myapp Enable strict mode in CI so any build failure during packaging immediately surfaces as exit code 4 rather than a silent partial result.
copy
$ veracode package --strict ./myapp
Adds veracode fix sca command to generate fixes for vulnerable dependencies identified in SCA scans (Limited Availability).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds --exclude flag to veracode package to prevent specified Java packages or JAR files from being scanned. Adds --skip-packagers flag to veracode package to exclude specific artifacts (e.g. unsupported SQL) from packaging results without affecting other languages. Adds VERACODE_PACKAGE_GOLANG_GENERATE environment variable to enable client-side CGO code generation when packaging Go applications. Adds SRCLR_MAKE_WINDOWS environment variable to enable preprocessing C/C++ source files with Make on Windows using a native Windows gcc or clang compiler.
+21 more
show less
Adds --strict flag to veracode package: when enabled, returns exit code 4 for any build failures during packaging. Introduces veracode package discover command to detect toolchains required to successfully create scannable artifacts. Introduces veracode auth login command to onboard new users via OAuth2 OAuth2 An open authorization framework (RFC 6749) that lets a service grant limited access to a user's resources on another service without exposing credentials, giving cyber tools a standard way to authenticate against third-party APIs. Adds veracode dynamic scan support for target UUIDs UUIDs A universally unique identifier, usually a 128-bit value used to identify an object across systems. It is designed to make independently generated identifiers unlikely to collide. Introduces exit codes 5, 6, and 7 for veracode package to improve CI/CD pipeline automation and error handling. Introduces exit codes for veracode package discover. Enables veracode scan to apply a custom policy defined in the Veracode Platform and view policy evaluation for individual findings. Adds SBOM generation via veracode sca agent-based scans, with output in CycloneDX 1.6 CycloneDX 1.6 An OWASP-maintained Software Bill of Materials standard that catalogs components, dependencies, and supply-chain metadata; tools use it to produce or consume machine-readable SBOMs in a widely supported schema. SPDX 2.3 SPDX 2.3 An open standard from the Linux Foundation for describing software bills of materials, letting cyber tools exchange dependency, license, and vulnerability data in a common machine-readable format. Adds requirements-dev.txt support in Python packaging workflows to include development dependencies. Enables veracode scan to specify a custom location from which vulnerability databases can be downloaded. Adds Dockerfile heredoc syntax parsing support to veracode scan. Adds veracode package discover toolchain detection for Java projects using Gradle. Adds veracode package discover toolchain detection for JavaScript projects using npm or Yarn. Categorizes secret-type findings as Critical in veracode scan results. Prioritizes vulnerability results from the NVD NVD The National Vulnerability Database, maintained by NIST, is the U.S. government repository of CVE records enriched with CVSS scores and metadata; cyber tools query it to drive vulnerability prioritization. veracode scan when available. Adds support for the Poetry package management tool in Python autopackaging. Adds support for preprocessing C/C++ source code on Linux via veracode package, replacing the existing Linux autopackaging solution. Adds support for preprocessor header files (PCH) and processing all Makefiles in a directory tree in veracode package. Creates a separate asset for each repository in the ADO workflow in veracode scan. Introduces schema enhancements for container and IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. veracode scan. Adds support for Go v1.24 in veracode package.
Adds veracode fix sca command to generate fixes for vulnerable dependencies identified in SCA scans (Limited Availability).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Introduces veracode package discover command to detect toolchains required to successfully create scannable artifacts. Introduces veracode auth login command to onboard new users via OAuth2 OAuth2 An open authorization framework (RFC 6749) that lets a service grant limited access to a user's resources on another service without exposing credentials, giving cyber tools a standard way to authenticate against third-party APIs. Adds SBOM generation via veracode sca agent-based scans, with output in CycloneDX 1.6 CycloneDX 1.6 An OWASP-maintained Software Bill of Materials standard that catalogs components, dependencies, and supply-chain metadata; tools use it to produce or consume machine-readable SBOMs in a widely supported schema. SPDX 2.3 SPDX 2.3 An open standard from the Linux Foundation for describing software bills of materials, letting cyber tools exchange dependency, license, and vulnerability data in a common machine-readable format.
22 more in Everything
Static Analysis updates (2026-09-23)
Sep 23, 2026
·
issue 084
Veracode Static Analysis adds iOS 27, Go 1.27, DryRun Security integration, and Pipeline Scan support for artifacts larger than 200 MB︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Adds support for excluding Java .jar files from static analysis using veracode.json.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds support for excluding specific Java classes from Static Analysis through the veracode.json configuration file. Pipeline Scan now supports scanning packaged artifacts larger than 200 MB with no changes to existing integrations required. Adds support for Dart 3.13 and Flutter 3.47. Adds support for Android 17.
+30 more
show less
Adds support for Next.js 16.x. Adds support for the Python google-cloud-bigquery library. Enhances the Python scanner with improved taint tracking, cross-file analysis, and pattern recognition, and adds support for PySpark, Flask, Django, and FastAPI applications. Adds support for Dart 3.12 and Flutter 3.44. Adds support for Kotlin 2.4. Adds support for the CloudKit framework on Apple platforms. Adds support for Apple Security framework APIs. Adds support for JDK 25 (enhanced support). Adds support for applications built with Xcode 26.4. Adds support for scanning Java source code. Adds support for viewing Java source code on the platform. Expands hardcoded secrets detection to include application configuration files with -local and -prod naming patterns. Adds support for React 19. Adds support for Kotlin 2.3. Adds support for Psycopg 3 in Python applications. Adds support for Fast HTTP in Go. Adds support for Angular 20. Adds support for Next.js 15.x. Adds taint sinks for the send_from_directory and send_file functions in Python. Adds support for PyYAML in Python. Adds support for Apex 64 and Apex 65. Adds support for Spring Boot 4, Spring Core 7, and Spring Security 7 in Java. Adds support for the Svelte framework in JavaScript. Adds support for Ruby 4.0 and Rails 8.1. Adds support for Dart 3.10 and Flutter 3.38. Adds support for the Go Fiber web framework. Adds support for AWS Glue in Python. Adds support for Dart 3.11 and Flutter 3.41. Adds taint propagation support for the Swift standard library. Expands .NET taint sink coverage for CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. System.Web.UI.Page.Title and System.Web.UI.HtmlControls.HtmlHead.Title.
Adds support for excluding Java .jar files from static analysis using veracode.json.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds support for excluding specific Java classes from Static Analysis through the veracode.json configuration file. Adds support for Android 17. Adds support for the Python google-cloud-bigquery library. Adds support for the CloudKit framework on Apple platforms.
+9 more
show less
Adds support for Apple Security framework APIs. Adds support for scanning Java source code. Adds support for viewing Java source code on the platform. Adds support for Psycopg 3 in Python applications. Adds support for Fast HTTP in Go. Adds support for PyYAML in Python. Adds support for the Svelte framework in JavaScript. Adds support for the Go Fiber web framework. Adds support for AWS Glue in Python.
21 more in Everything
DAST updates (2026-09-23)
Sep 23, 2026
·
issue 083
Veracode DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces. EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do.
Supports assigning multiple teams to a single DAST target when creating a web application or API specification, enabling shared security ownership.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds the ability to select a business unit when creating a web application or API specification target, or on the DAST configuration page. Adds Directory Restrictions to DAST target configuration to control scan scope. Introduces custom host-to-IP address mappings for DAST scans when DNS lookup is unavailable or not desired. Dynamic Analysis and DAST Enterprise mode now support scanning web applications for open ports.
+16 more
show less
Adds new detections for HTTP headers, TLS, and fingerprinting in the scan engine. EASM now automatically creates discovered targets in DAST, which can be mapped or converted to regular DAST targets for scanning. DAST Enterprise mode now supports downloadable scan reports providing visibility into scan coverage and scanner behavior. DAST Enterprise mode now provides an AI-based authentication method (AI-Assisted Login ) to cover complex login flows without recorded login scripts. DAST now supports manual application linking to connect analysis run results to a Veracode Platform application for policy evaluation and combined multi-scan-type reporting. The ISM endpoint 24.10.0 introduces a proxy exclusion list allowing specified hosts to bypass the configured proxy settings. The DAST Target Configuration Service REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. API Scanning now supports uploading and scanning Postman Collections in the Veracode Platform. Web application and API scans now support time-based one-time password (TOTP TOTP A one-time password algorithm (RFC 6238) that generates short-lived codes from a shared secret and the current time, giving cyber tools phishing-resistant second-factor authentication without a server round-trip. multi-factor authentication multi-factor authentication Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. Web application and API scans now support custom cookies for authentication. Adds the ability to set URL scan settings at the organization level via the Dynamic Analysis REST API. API Scanning adds Scriptable Request Modification (SRM), allowing JavaScript to modify HTTP requests at runtime during authentication. Adds a similarity threshold setting for web application analyses to ignore similar web pages during scanning. Adds the ability to schedule an analysis pause and resume on specific days of the week, during specific periods, or both. DAST Enterprise mode adds support for login scripts, scanner variables, client certificates, and Scriptable Request Modifications (SRM) for APIs as additional authentication configuration options. DAST Enterprise mode adds Internal Scanning Management (ISM) support for scanning web applications and APIs behind a corporate firewall.
Supports assigning multiple teams to a single DAST target when creating a web application or API specification, enabling shared security ownership.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds Directory Restrictions to DAST target configuration to control scan scope. Introduces custom host-to-IP address mappings for DAST scans when DNS lookup is unavailable or not desired. Dynamic Analysis and DAST Enterprise mode now support scanning web applications for open ports. Adds new detections for HTTP headers, TLS, and fingerprinting in the scan engine.
+14 more
show less
EASM now automatically creates discovered targets in DAST, which can be mapped or converted to regular DAST targets for scanning. DAST Enterprise mode now supports downloadable scan reports providing visibility into scan coverage and scanner behavior. DAST Enterprise mode now provides an AI-based authentication method (AI-Assisted Login ) to cover complex login flows without recorded login scripts. DAST now supports manual application linking to connect analysis run results to a Veracode Platform application for policy evaluation and combined multi-scan-type reporting. The ISM endpoint 24.10.0 introduces a proxy exclusion list allowing specified hosts to bypass the configured proxy settings. The DAST Target Configuration Service REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. API Scanning now supports uploading and scanning Postman Collections in the Veracode Platform. Web application and API scans now support time-based one-time password (TOTP TOTP A one-time password algorithm (RFC 6238) that generates short-lived codes from a shared secret and the current time, giving cyber tools phishing-resistant second-factor authentication without a server round-trip. multi-factor authentication multi-factor authentication Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. Web application and API scans now support custom cookies for authentication. Adds the ability to set URL scan settings at the organization level via the Dynamic Analysis REST API. API Scanning adds Scriptable Request Modification (SRM), allowing JavaScript to modify HTTP requests at runtime during authentication. Adds a similarity threshold setting for web application analyses to ignore similar web pages during scanning. DAST Enterprise mode adds support for login scripts, scanner variables, client certificates, and Scriptable Request Modifications (SRM) for APIs as additional authentication configuration options. DAST Enterprise mode adds Internal Scanning Management (ISM) support for scanning web applications and APIs behind a corporate firewall.
2 more in Everything
└──▷ BREAKING ON UPGRADE
! The DAST scheduling API endpoints have changed as part of the enhanced scheduling rollout; integrations using the REST API to manage schedules must be updated to use the new endpoints per the DAST API specification.
Veracode allows assigning multiple teams to DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
└──▷ HOW TO FIND IT
Collaborate on security ownership by assigning multiple teams during DAST target creation.
📍 In the console, go to Applications › Web Applications (or APIs) and select Create New . In the target settings, assign the desired multiple teams before saving.
Assign multiple teams to a DAST target when creating a web application or API specification
1 detail in Everything
Assign multiple teams for DAST targets
Sep 23, 2026
· release notes
Allow assigning multiple teams to DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Adds the ability to assign multiple teams to a DAST target when creating a web application or API specification.
1 detail in Everything
Veracode adds Jira 11 support, a redesigned EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do.
Veracode Integration for Jira Server v5.0.2 adds support for Jira 11, including Java 21 and platform compatibility with Jira 11.3.10.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enhanced Python scanner now uses each application's initial scan baseline for consistent flaw matching across subsequent scans.
Veracode Integration for Jira Server v5.0.2 adds support for Jira 11, including Java 21 and platform compatibility with Jira 11.3.10.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
1 more in Everything
└──▷ BREAKING ON UPGRADE
! Customers who transitioned to the enhanced Python scanner on July 22, 2026 may find that previously identified flaws no longer match historical findings and previously applied mitigations may need to be reapplied.
EASM updates (2026-09-21)
Sep 21, 2026
·
issue 081
Veracode EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do.
└──▷ HOW TO FIND IT
Promote a discovered web application to a DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
📍 In the EASM UI, open the asset you want to scan, mark it as a DAST Candidate , then navigate to DAST Essentials to find the asset listed as a discovered target ready for scanning.
Adds real-time in-app notifications when scans complete, fail, or are cancelled.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds multi-project visibility for centralized risk management across all projects. Adds scan scheduling to streamline scan orchestration across projects. Adds AI-powered intelligence for accelerated risk prioritization. Introduces redesigned EASM UI with improved navigation and usability, with the Legacy UI still available.
+5 more
show less
Adds a Findings view to surface large volumes of security data as actionable insights with prioritization workflows and expanded reporting. Adds Issues capability to streamline remediation efforts and improve focus on cyber hygiene. Adds Dashboard widgets — Heatmap, World map, and Things — with filterable data views and a shortcut to create reports. Adds Business Units management, enabling creation, assignment, and domain association. Enables export of web applications from EASM directly into DAST Essentials by marking assets as DAST Candidates to create discovered targets for DAST scanning.
Adds real-time in-app notifications when scans complete, fail, or are cancelled.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds multi-project visibility for centralized risk management across all projects. Adds scan scheduling to streamline scan orchestration across projects. Adds AI-powered intelligence for accelerated risk prioritization. Adds a Findings view to surface large volumes of security data as actionable insights with prioritization workflows and expanded reporting.
+3 more
show less
Adds Issues capability to streamline remediation efforts and improve focus on cyber hygiene. Adds Business Units management, enabling creation, assignment, and domain association. Enables export of web applications from EASM directly into DAST Essentials by marking assets as DAST Candidates to create discovered targets for DAST scanning.
2 more in Everything
Static Analysis updates (2026-09-16)
Sep 16, 2026
·
issue 077
Veracode: Skips @isTest methods during Apex scans to reduce noise and improve result quality.
Integration updates (2026-09-16)
Sep 16, 2026
·
issue 077
Veracode integrations gain GitHub Fix for SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
└──▷ USE IT
Run scheduled scans against a long-lived analysis branch rather than the repository default branch in Azure DevOps.
veracode.yml
copy
analysis_branch: release/2026-q3
Adds support for custom predependency commands in the Veracode YAML file to prepare projects before scanning (GitHub Workflow Integration v2.1.3).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds a custom agent pool name parameter in veracode.yml to specify the agent pool for pipeline execution (Azure DevOps Workflow Integration v2.4.3). Adds analysis_branch support in veracode.yml so scheduled scans run for the specified analysis branch instead of the default branch (Azure DevOps Workflow Integration v2.3.10). Adds page size support to the Platform Applications API (/appsec/v1/applications) for efficient retrieval of large application lists (Java API Wrapper v26.3.19.0). Introduces support for the Veracode Platform paginated Sandbox REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
+13 more
show less
Adds a Current File filter to Static Scan Findings in Veracode Scan for VS Code, allowing you to view findings only for the file currently open in the editor. Adds an option to filter and group Static Scan Findings by file name in Veracode Scan for VS Code, with findings for each file grouped by severity. Adds an option to change the region during OAuth authentication in Veracode Scan for VS Code, displaying the current or most recently used region. Adds a Scan Scope setting in Veracode Scan for Visual Studio to scan the full project directory or only the active solution for faster, more focused results. Enables installation and configuration of the Veracode GitHub Integration directly from the Veracode Platform, eliminating manual GitHub Marketplace steps. Enables scheduling of Static Analysis, SCA, and Infrastructure as Code (IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Adds a new uninstallation workflow on the Veracode Platform to uninstall the Veracode app from GitHub organizations. Enables scheduling scans for every organization in which the Azure DevOps Workflow Integration is installed, based on veracode.yml configurations. Adds usage analytics in Veracode Scan for JetBrains v1.8.0 to provide insights into plugin adoption, feature usage, and scan activity. Adds usage analytics in Veracode Scan for Visual Studio v0.8.0 to provide insights into plugin adoption, feature usage, and scan activity. Adds usage analytics in Veracode Scan for VS Code v1.16.0 to provide insights into plugin adoption, feature usage, and scan activity. Adds support for Jira 11, including required Java 21 and platform compatibility updates (Veracode Integration for Jira Server v5.0.2). Adds support for Visual Studio 2026 in Veracode Scan for Visual Studio v0.7.2.
Adds support for custom predependency commands in the Veracode YAML file to prepare projects before scanning (GitHub Workflow Integration v2.1.3).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds a custom agent pool name parameter in veracode.yml to specify the agent pool for pipeline execution (Azure DevOps Workflow Integration v2.4.3). Introduces support for the Veracode Platform paginated Sandbox REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Adds a Current File filter to Static Scan Findings in Veracode Scan for VS Code, allowing you to view findings only for the file currently open in the editor. Adds an option to change the region during OAuth authentication in Veracode Scan for VS Code, displaying the current or most recently used region.
+8 more
show less
Adds a Scan Scope setting in Veracode Scan for Visual Studio to scan the full project directory or only the active solution for faster, more focused results. Enables installation and configuration of the Veracode GitHub Integration directly from the Veracode Platform, eliminating manual GitHub Marketplace steps. Enables scheduling of Static Analysis, SCA, and Infrastructure as Code (IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Adds a new uninstallation workflow on the Veracode Platform to uninstall the Veracode app from GitHub organizations. Enables scheduling scans for every organization in which the Azure DevOps Workflow Integration is installed, based on veracode.yml configurations. Adds usage analytics in Veracode Scan for JetBrains v1.8.0 to provide insights into plugin adoption, feature usage, and scan activity. Adds usage analytics in Veracode Scan for Visual Studio v0.8.0 to provide insights into plugin adoption, feature usage, and scan activity. Adds usage analytics in Veracode Scan for VS Code v1.16.0 to provide insights into plugin adoption, feature usage, and scan activity.
5 more in Everything
└──▷ BREAKING ON UPGRADE
! The Veracode Flaw Importer task (which contains spaces in the task name) is deprecated and replaced by VeracodeFlawImporter in Veracode Azure DevOps extension v3.35.0; the deprecated task is scheduled for removal in a future release.! Veracode will end support for the Veracode Integration for Jira on Jira Server and Jira Data Center 9.x on November 30, 2026; upgrade to Jira 10 or later to remain supported.
Veracode adds policy parameter to veracode.yml for IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup.
Veracode Static Analysis integration with DryRun Security
Sep 16, 2026
· release notes
Veracode Static Analysis integrates with DryRun Security to surface findings in AI-native PR workflows.
Integrates Veracode Static Analysis findings into DryRun Security analysis and developer workflows. Surfaces security context during pull request and code review workflows. Provides Veracode findings as trusted security signals and remediation guidance for AI-assisted development tools.
3 details in Everything
Veracode Integration for Jira Server v5.0.2
Sep 16, 2026
· release notes
Veracode Integration for Jira Server v5.0.2 adds Jira 11 and Java 21 support
Adds support for Jira 11 platform compatibility Updates workflows to improve stability with Jira 11.3.10
2 details in Everything
Azure DevOps Workflow Integration v2.4.4
Sep 15, 2026
· release notes
Adds predependency_command parameter to veracode.yml for pre-package execution
└──▷ TRY IT
After an SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
└──▷ BREAKING ON UPGRADE
! Veracode eLearning REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Veracode adds veracode fix sca CLI command, IDE/CLI Usage Analytics dashboard, Dart 3.13, Flutter 3.47, PHP 8.4/8.5 support, and GitHub Workflow SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
└──▷ TRY IT
Remediate vulnerable SCA dependencies identified in a scan by generating patches and safe upgrade paths directly from the CLI.
Adds support for Dart 3.13 and Flutter 3.47 in Static Analysis. Adds support for PHP 8.4 and PHP 8.5 in Static Analysis. Improves detection of CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. useState in Static Analysis.
3 more in Everything
└──▷ BREAKING ON UPGRADE
! The Veracode eLearning REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Veracode adds Fix for SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. veracode fix sca CLI command, IDE/CLI Usage Analytics, and Dart/Flutter/PHP static analysis support.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
└──▷ TRY IT
After an SCA scan surfaces vulnerable dependencies, automatically generate a remediation patch and safe upgrade path without manually researching fixes.
Adds veracode fix sca CLI command to analyze vulnerable dependencies from SCA findings, generate remediation patches, and identify safe upgrade paths (Limited Availability).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds IDE and CLI Usage Explore and Dashboard in Veracode Analytics to visualize and explore organization-wide IDE and CLI usage.
2 details in Everything
Training updates (2026-09-10)
Sep 10, 2026
·
issue 072
Veracode training adds LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code. OWASP Top 10:2025 OWASP Top 10:2025 A ranked list of the ten most critical web application risk categories, maintained by the Open Worldwide Application Security Project, used by cyber tools to prioritize detection, testing, and remediation coverage. Platform SSO Platform SSO A macOS framework from Apple that lets identity providers hook into the operating system login flow, enabling enterprise single sign-on at the platform level rather than per-app.
Adds updatedAfter parameter to the Get Lesson Progress API to support incremental loads of lesson progress data.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds excludeNotStarted=true parameter to the Get Lesson Progress API to filter out lessons that have not been started. Adds stack field and updated_on field to the Get Lesson Progress API response. Get Lesson Progress API now returns Not Started status when both start_time and end_time are null. Integrates Security Labs user and team management with the Veracode Platform, authenticating Security Labs users through Veracode IAM IAM Identity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access.
+10 more
show less
Adds team search capability for Security Labs administrators and managers in Security Labs. Adds full OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. Adds new eLearning courses aligned to OWASP Top 10:2025 for .NET, Java, JavaScript, PHP, Python, and general Software Security Awareness, available with English, Spanish, French, Portuguese, and Chinese captions. Adds skills assessment quiz courses for Static Analysis, Dynamic Analysis, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. Adds Container Security in Docker lesson series covering capabilities, users, networking, virtualization, resources, orchestration, and inventory topics. Adds in-app guidance for creating campaigns and using reporting in Security Labs. Adds CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. CWEs CWEs A community-maintained list of software and hardware weakness types, maintained by MITRE, that gives cyber tools a standard taxonomy for classifying and communicating vulnerability root causes. Adds code syntax highlighting tailored to programming languages in Security Labs lessons. Extends eLearning report date range selection to up to one year in the past. Upgrades OWASP API Security Top 10 coverage in Security Labs from the 2019 list to the 2023 list, adding lessons for three new categories (API 6, API 7, API 10).
Adds updatedAfter parameter to the Get Lesson Progress API to support incremental loads of lesson progress data.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Integrates Security Labs user and team management with the Veracode Platform, authenticating Security Labs users through Veracode IAM IAM Identity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access. Adds team search capability for Security Labs administrators and managers in Security Labs. Adds full OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. Adds new eLearning courses aligned to OWASP Top 10:2025 for .NET, Java, JavaScript, PHP, Python, and general Software Security Awareness, available with English, Spanish, French, Portuguese, and Chinese captions.
+5 more
show less
Adds skills assessment quiz courses for Static Analysis, Dynamic Analysis, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. Adds Container Security in Docker lesson series covering capabilities, users, networking, virtualization, resources, orchestration, and inventory topics. Adds in-app guidance for creating campaigns and using reporting in Security Labs. Adds CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. CWEs CWEs A community-maintained list of software and hardware weakness types, maintained by MITRE, that gives cyber tools a standard taxonomy for classifying and communicating vulnerability root causes. Adds code syntax highlighting tailored to programming languages in Security Labs lessons.
5 more in Everything
└──▷ BREAKING ON UPGRADE
! The Veracode eLearning REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. ! The Security Labs default URL has changed from https://securitylabs.veracode.com/ to https://securitylabs.veracode.com/security-labs/ — customers using SSO must update their configured Security Labs URL.! In Security Labs, Teams are renamed to Organizations and Roles are renamed to Teams — any documentation, integrations, or scripts referencing the old terminology must be updated.! 33 deprecated eLearning courses (OWASP 2017, OWASP Top 10 (2021), and Secure Coding for .NET/.Java/.JavaScript/.PHP/.Python (6 courses each, 3 for Python)) are no longer available; certification levels have been updated to include newer replacement courses.! OWASP Top 10 (2021) Security Labs lessons are no longer available following their deprecation.
Veracode Fix adds AI-assisted remediation across IDE, CLI, and SCM SCM Source Code Management: version-control systems (Git, SVN, etc.) that track changes to code over time, giving cyber tools reproducible builds, audit trails, and collaborative development workflows. SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment. SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
└──▷ TRY IT
Run Fix for SCA in a CI pipeline, where the remote backend sandbox handles transitive dependencies and batches findings comprehensively.
copy
$ veracode fix --remote
Adds --remote flag requirement for Fix for SCA via the Veracode CLI, enabling backend sandbox execution with full source access for automated CI pipelines, scheduled jobs, and SCM workflows. Supports Fix for SAST in Eclipse, JetBrains, Visual Studio, and VS Code IDEs for interactive in-editor remediation. Supports Fix for SCA via SCM integration (Fix in SCM ) that scans a repository, generates patches, and opens merge requests automatically. Supports Fix for SAST and Fix for SCA via the Veracode CLI (Fix in CLI ) for both interactive use and automated scripting in CI pipelines.
4 details in Everything
Training updates (2026-09-09)
Sep 9, 2026
·
issue 069
Veracode training adds LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code. OWASP Top 10:2025 OWASP Top 10:2025 A ranked list of the ten most critical web application risk categories, maintained by the Open Worldwide Application Security Project, used by cyber tools to prioritize detection, testing, and remediation coverage.
Adds updatedAfter parameter to the Get Lesson Progress API to support incremental data loads. Adds excludeNotStarted=true parameter to the Get Lesson Progress API to filter out lessons that have not been started. Adds stack field and updated_on field to the Get Lesson Progress API response, and surfaces a Not Started status when both start_time and end_time are null. Integrates Security Labs user and team management into the Veracode Platform, with authentication routed through Veracode IAM IAM Identity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access. Adds team search capability for Security Labs administrators and managers.
+9 more
show less
Adds eLearning date-range filter allowing report start dates up to one year in the past. Adds six new OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. Adds complete OWASP Top 10:2025 Security Labs lab series (A01–A10), including two new categories: A03 Software Supply Chain Failures and A10 Mishandling of Exceptional Conditions. Adds Container Security in Docker Security Labs lesson track spanning Capabilities, Users, Virtualization, Networking, Resources, Orchestration, and Inventory topics. Adds in-app guidance in Security Labs for creating campaigns and using reporting. Adds CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. Adds code syntax highlighting to Security Labs lessons, tailored to the programming language of each code sample. Adds OWASP API Top 10 2023 Security Labs lessons, upgrading coverage from the 2019 list and adding three new categories (API 6, API 7, API 10) in Java, Node, and .NET. Adds five assessment quiz eLearning courses (User and application setup, Static Analysis, Dynamic Analysis, Scan and fix in your IDE, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Integrates Security Labs user and team management into the Veracode Platform, with authentication routed through Veracode IAM IAM Identity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access. Adds team search capability for Security Labs administrators and managers. Adds six new OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. Adds complete OWASP Top 10:2025 Security Labs lab series (A01–A10), including two new categories: A03 Software Supply Chain Failures and A10 Mishandling of Exceptional Conditions. Adds Container Security in Docker Security Labs lesson track spanning Capabilities, Users, Virtualization, Networking, Resources, Orchestration, and Inventory topics.
+5 more
show less
Adds in-app guidance in Security Labs for creating campaigns and using reporting. Adds CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. Adds code syntax highlighting to Security Labs lessons, tailored to the programming language of each code sample. Adds OWASP API Top 10 2023 Security Labs lessons, upgrading coverage from the 2019 list and adding three new categories (API 6, API 7, API 10) in Java, Node, and .NET. Adds five assessment quiz eLearning courses (User and application setup, Static Analysis, Dynamic Analysis, Scan and fix in your IDE, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
4 more in Everything
└──▷ BREAKING ON UPGRADE
! The default Security Labs URL has changed from https://securitylabs.veracode.com/ to https://securitylabs.veracode.com/security-labs/ — organizations using SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. ! In Security Labs, Teams are renamed to Organizations and Roles are renamed to Teams — any documentation, scripts, or integrations referencing these terms must be updated.! 33 deprecated eLearning courses (OWASP 2017, OWASP Top 10 2021, Secure Coding for .NET/Java/JavaScript/PHP/Python — 6 courses each, Secure Coding for Python — 3 courses) are no longer available as of June 2026; certification levels have been updated to reference the replacement OWASP Top 10:2025 courses.! OWASP Top 10 (2021) Security Labs lessons are no longer available as of June 2026.
Fix updates (2026-09-08)
Sep 8, 2026
·
issue 069
Veracode Fix gains SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. veracode fix sca CLI command, analyzing vulnerable dependencies and suggesting safe upgrade paths.
└──▷ TRY IT
Automatically generate a remediation patch for a vulnerable dependency identified in an SCA scan, so you can apply a safe upgrade without manually researching fix paths.
Adds veracode fix sca CLI command (and source control management integration) to analyze SCA findings, generate remediation patches, and identify safe dependency upgrade paths (Limited Availability). Adds COBOL support with fix suggestions for CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
2 details in Everything
Integration updates (2026-09-08)
Sep 8, 2026
·
issue 069
Veracode integrations gain Fix for SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
└──▷ USE IT
Enable verbose debug output in an Azure DevOps Workflow Integration pipeline to troubleshoot scan failures.
veracode.yml
copy
debug: true
Run scheduled Azure DevOps scans against a specific analysis branch rather than the repository default branch.
veracode.yml
copy
analysis_branch: main-security-scan
Adds custom agent pool name parameter in veracode.yml for Azure DevOps Workflow Integration v2.4.3 to specify the agent pool used for pipeline execution. Implements a configurable retry mechanism for the Veracode Platform Applications API (appsec/v1/applications) in Java API Wrapper v26.2.18.0 to handle transient failures, timeouts, and network issues. GitHub Workflow Integration now supports Veracode Fix for SCA, generating fixes for vulnerable dependencies identified in SCA scans. GitHub Workflow Integration v2.0.0 enables install, configuration, and credential updates for the GitHub Integration directly from the Veracode Platform, eliminating manual GitHub Marketplace steps. GitHub Workflow Integration v2.0.0 adds autopackaging support for Apex, VB6, and Perl.
+3 more
show less
GitHub Workflow Integration v2.0.0 adds the ability to schedule Static Analysis, SCA, and IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. GitHub Workflow Integration v2.1.1 adds a new uninstallation workflow on the Veracode Platform for removing the Veracode app from GitHub organizations. Adds support for Visual Studio 2026 in Veracode Scan for Visual Studio v0.7.2.
Adds custom agent pool name parameter in veracode.yml for Azure DevOps Workflow Integration v2.4.3 to specify the agent pool used for pipeline execution. GitHub Workflow Integration now supports Veracode Fix for SCA, generating fixes for vulnerable dependencies identified in SCA scans. GitHub Workflow Integration v2.0.0 enables install, configuration, and credential updates for the GitHub Integration directly from the Veracode Platform, eliminating manual GitHub Marketplace steps. GitHub Workflow Integration v2.0.0 adds the ability to schedule Static Analysis, SCA, and IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. GitHub Workflow Integration v2.1.1 adds a new uninstallation workflow on the Veracode Platform for removing the Veracode app from GitHub organizations.
+1 more
show less
Adds support for Visual Studio 2026 in Veracode Scan for Visual Studio v0.7.2.
2 more in Everything
Platform updates (2026-09-08)
Sep 8, 2026
·
issue 068
Veracode adds IDE/CLI usage analytics, a Custom PDF REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. XML APIs XML APIs Interfaces for reading, writing, or querying XML documents, provided by libraries such as libxml2 or built into language runtimes; cyber tools use them to parse structured data like configs, reports, or protocol messages reliably.
Adds the Custom PDF REST API to programmatically generate custom PDF reports. Adds support for OAuth Client Credentials authentication with the Veracode XML APIs (previously REST APIs REST APIs A convention for building HTTP-based interfaces where resources are addressed by URL and manipulated with standard verbs like GET, POST, and DELETE, giving cyber tools a predictable way to integrate with external services. Adds the most_recent_scan filter to the Reporting API Scans report; when set to true, returns only the most recent scan per asset. Adds the custom_severity filter to the Reporting API Findings report. Adds the action_type filter to the Reporting API Audit Log report to retrieve audit log records based on specific user actions.
+14 more
show less
Adds the collections_list field to the Finding Reporting API response, returning a list of collection names associated with the application. Adds the library_instance_ref field to the Veracode Reporting API findings response to uniquely identify the specific library instance associated with a finding. Adds the data_refresh_date field to the Reporting API to indicate the most recent time Analytics data was refreshed. Introduces a new IDE and CLI Usage Explore and Dashboard in Veracode Analytics to visualize organization-wide IDE and CLI plugin usage. Adds Firewall Usage Explore and Dashboard to Veracode Analytics, surfacing metrics for Veracode Firewall. Adds Collections fields to the Applications explore in Veracode Analytics, including new Collections visualizations in the Policy Compliance Overview dashboard. Introduces a new Audit Log report in the Reporting REST API to query detailed user activity from Veracode Analytics. Adds support for creating and managing OAuth 2.0 OAuth 2.0 An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms. Enables mapping multiple domains to a single identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. SP-initiated SP-initiated A SAML or OAuth/OIDC login flow where the Service Provider redirects the user to an Identity Provider to authenticate, rather than the IdP pushing an assertion unprompted; tools use it to trigger SSO from their own login page. SAML SSO SAML SSO An authentication protocol that lets a user log in once with an identity provider and access multiple services without re-entering credentials, by passing signed XML assertions between parties. Adds the ability to disable Veracode-defined roles for users who use custom roles, via the Identity API. Makes container and IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Introduces Manual Penetration Testing (MPT) Flaw Matching to correlate findings across tests for consistent flaw IDs, status values, and remediation grace period support. Adds six new built-in security policies to the Veracode Platform. Updates the Auto-Update OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. OWASP Top 10:2025 OWASP Top 10:2025 A ranked list of the ten most critical web application risk categories, maintained by the Open Worldwide Application Security Project, used by cyber tools to prioritize detection, testing, and remediation coverage. MITRE MITRE A US federally funded research and development center that maintains public frameworks—ATT&CK, CVE, D3FEND—that cyber tools use to classify threats, vulnerabilities, and defensive techniques in a common language.
Adds the Custom PDF REST API to programmatically generate custom PDF reports. Adds support for OAuth Client Credentials authentication with the Veracode XML APIs (previously REST APIs REST APIs A convention for building HTTP-based interfaces where resources are addressed by URL and manipulated with standard verbs like GET, POST, and DELETE, giving cyber tools a predictable way to integrate with external services. Introduces a new IDE and CLI Usage Explore and Dashboard in Veracode Analytics to visualize organization-wide IDE and CLI plugin usage. Adds Firewall Usage Explore and Dashboard to Veracode Analytics, surfacing metrics for Veracode Firewall. Introduces a new Audit Log report in the Reporting REST API to query detailed user activity from Veracode Analytics.
+6 more
show less
Adds support for creating and managing OAuth 2.0 OAuth 2.0 An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms. Enables mapping multiple domains to a single identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. SP-initiated SP-initiated A SAML or OAuth/OIDC login flow where the Service Provider redirects the user to an Identity Provider to authenticate, rather than the IdP pushing an assertion unprompted; tools use it to trigger SSO from their own login page. SAML SSO SAML SSO An authentication protocol that lets a user log in once with an identity provider and access multiple services without re-entering credentials, by passing signed XML assertions between parties. Adds the ability to disable Veracode-defined roles for users who use custom roles, via the Identity API. Makes container and IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Introduces Manual Penetration Testing (MPT) Flaw Matching to correlate findings across tests for consistent flaw IDs, status values, and remediation grace period support. Adds six new built-in security policies to the Veracode Platform.
8 more in Everything
└──▷ BREAKING ON UPGRADE
! The Veracode Healthcheck endpoint /healthcheck/status has been removed and now returns a 404 error; use the v2/principal endpoint in the Identity REST API instead.
Veracode adds limited availability veracode fix sca CLI command for SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds the veracode fix sca subcommand to the Veracode CLI for analyzing vulnerable dependencies and generating remediation patches Enables integration with source control management systems for automated safe upgrade paths
2 details in Everything
GitHub Workflow Integration now supports Veracode Fix for SCA
Sep 8, 2026
· release notes
GitHub Workflow Integration now generates fixes for vulnerable dependencies in SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Integration updates (2026-09-07)
Sep 7, 2026
·
issue 068
Veracode integrations gain GitHub Platform install, scan scheduling, VS Code file filters, ADO agent pool config, and expanded API pagination support.
└──▷ USE IT
Enable verbose debug output in a GitHub or Azure DevOps pipeline to diagnose scan failures without modifying pipeline code.
veracode.yml
copy
# In veracode.yml
debug: true
Pin scheduled ADO scans to a specific long-lived branch rather than the repo default, useful for release-branch gating.
veracode.yml
copy
# In veracode.yml
analysis_branch: release/2026-q3
Adds debug configuration option in veracode.yml for debugging and troubleshooting pipeline runs (GitHub Workflow Integration v1.0.6, Azure DevOps Workflow Integration v2.3.6). Adds analysis_branch support in veracode.yml so scheduled scans run against a specified branch instead of the default branch (Azure DevOps Workflow Integration v2.3.10). Adds custom agent pool name parameter in veracode.yml to specify the agent pool used for pipeline execution (Azure DevOps Workflow Integration v2.4.3). Adds support for custom predependency commands in the Veracode YAML file to prepare projects before scanning (GitHub Workflow Integration v2.1.3). Adds page size support to the Platform Applications API (/appsec/v1/applications) to improve efficiency when retrieving large application lists (Java API Wrapper v26.3.19.0).
+16 more
show less
Adds support for the Veracode Platform Findings REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Introduces support for the Veracode Platform paginated Sandbox REST API, enabling retrieval of sandbox lists using pagination (Java API Wrapper v26.3.19.0). Adds a Current File filter to Static Scan Findings in VS Code, allowing you to view findings for the file currently open in the editor (Veracode Scan for VS Code v1.16.3). Adds an option to filter and group Static Scan Findings by file name in VS Code, with findings for each file grouped by severity (Veracode Scan for VS Code v1.16.3). Adds an option to change the region during OAuth authentication in VS Code, displaying the current or most recently used region (Veracode Scan for VS Code v1.16.3). Enables installing and configuring the Veracode GitHub Integration directly from the Veracode Platform, eliminating manual GitHub Marketplace installation steps (GitHub Workflow Integration v2.0.0). Enables scheduling Static Analysis, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Adds autopackaging support for Apex, VB6, and Perl in the GitHub Workflow Integration (GitHub Workflow Integration v2.0.0). Adds a new uninstallation workflow on the Veracode Platform to uninstall the Veracode app from GitHub organizations (GitHub Workflow Integration v2.1.1). Enables scheduling scans for every organization in which the Azure DevOps Workflow Integration is installed, based on veracode.yml configuration (Azure DevOps Workflow Integration v2.3.9). Adds a Scan Scope setting in Veracode Scan for Visual Studio to scan the full project directory or only the active solution (Veracode Scan for Visual Studio v0.8.0). Adds usage analytics to Veracode Scan for Visual Studio to provide insights into plugin adoption, feature usage, and scan activity (Veracode Scan for Visual Studio v0.8.0). Adds usage analytics to Veracode Scan for VS Code to provide insights into plugin adoption, feature usage, and scan activity (Veracode Scan for VS Code v1.16.0). Adds usage analytics to Veracode Scan for JetBrains to provide insights into plugin adoption, feature usage, and scan activity (Veracode Scan for JetBrains v1.8.0). Adds Visual Studio 2026 support to Veracode Scan for Visual Studio (Veracode Scan for Visual Studio v0.7.2). Implements a configurable retry mechanism for the Veracode Platform Applications API (appsec/v1/applications) to improve handling of transient failures and timeouts (Java API Wrapper v26.2.18.0).
Adds debug configuration option in veracode.yml for debugging and troubleshooting pipeline runs (GitHub Workflow Integration v1.0.6, Azure DevOps Workflow Integration v2.3.6). Adds analysis_branch support in veracode.yml so scheduled scans run against a specified branch instead of the default branch (Azure DevOps Workflow Integration v2.3.10). Adds custom agent pool name parameter in veracode.yml to specify the agent pool used for pipeline execution (Azure DevOps Workflow Integration v2.4.3). Adds support for custom predependency commands in the Veracode YAML file to prepare projects before scanning (GitHub Workflow Integration v2.1.3). Adds support for the Veracode Platform Findings REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
+12 more
show less
Introduces support for the Veracode Platform paginated Sandbox REST API, enabling retrieval of sandbox lists using pagination (Java API Wrapper v26.3.19.0). Adds a Current File filter to Static Scan Findings in VS Code, allowing you to view findings for the file currently open in the editor (Veracode Scan for VS Code v1.16.3). Adds an option to filter and group Static Scan Findings by file name in VS Code, with findings for each file grouped by severity (Veracode Scan for VS Code v1.16.3). Adds an option to change the region during OAuth authentication in VS Code, displaying the current or most recently used region (Veracode Scan for VS Code v1.16.3). Enables installing and configuring the Veracode GitHub Integration directly from the Veracode Platform, eliminating manual GitHub Marketplace installation steps (GitHub Workflow Integration v2.0.0). Enables scheduling Static Analysis, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Adds a new uninstallation workflow on the Veracode Platform to uninstall the Veracode app from GitHub organizations (GitHub Workflow Integration v2.1.1). Enables scheduling scans for every organization in which the Azure DevOps Workflow Integration is installed, based on veracode.yml configuration (Azure DevOps Workflow Integration v2.3.9). Adds a Scan Scope setting in Veracode Scan for Visual Studio to scan the full project directory or only the active solution (Veracode Scan for Visual Studio v0.8.0). Adds usage analytics to Veracode Scan for Visual Studio to provide insights into plugin adoption, feature usage, and scan activity (Veracode Scan for Visual Studio v0.8.0). Adds usage analytics to Veracode Scan for VS Code to provide insights into plugin adoption, feature usage, and scan activity (Veracode Scan for VS Code v1.16.0). Adds usage analytics to Veracode Scan for JetBrains to provide insights into plugin adoption, feature usage, and scan activity (Veracode Scan for JetBrains v1.8.0).
4 more in Everything
└──▷ BREAKING ON UPGRADE
! The Veracode Flaw Importer task (containing spaces in the task name) is deprecated and replaced by VeracodeFlawImporter in the Veracode Azure DevOps extension v3.35.0; the deprecated task is scheduled for removal in a future release.! Support for the Veracode Integration for Jira on Jira Server and Jira Data Center 9.x ends November 30, 2026 — upgrade to Jira 10 or later to maintain a supported configuration.
Static Analysis updates (2026-09-03)
Sep 3, 2026
·
issue 076
Veracode SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment.
Adds veracode.json support for excluding specific Java .jar files from static analysis.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds veracode.json support for excluding specific Java classes from Static Analysis. Expands hardcoded secrets detection to include application configuration files with -local and -prod naming patterns in Java. Adds send_from_directory and send_file as taint sinks for CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. Adds .NET Semantic Kernel (SK) InvocationFilter and Filter support for .NET SAST.
+53 more
show less
Updates Gen IR: the --capture flag now includes diagnostic data in .xcarchive files for iOS troubleshooting. Adds support for scanning packaged artifacts larger than 200 MB in Pipeline Scan. Adds support for Dart 3.13 and Flutter 3.47. Adds support for PHP 8.4 and PHP 8.5. Adds support for Android 17. Adds support for Next.js 16.x. Adds support for the Python google-cloud-bigquery library. Adds enhanced Python scanner with improved taint tracking, cross-file analysis, and pattern recognition, covering PySpark, Flask, Django, and FastAPI. Adds support for .NET 10. Adds support for Dart 3.12 and Flutter 3.44. Adds support for Kotlin 2.4. Adds support for the CloudKit framework for Apple Platforms. Adds support for Apple Security framework APIs. Adds support for applications built with Xcode 26.4. Adds support for JDK 26. Adds support for scanning Java source code. Adds support for viewing Java source code on the Veracode platform. Adds support for React 19. Adds support for Kotlin 2.3. Adds support for Psycopg 3 in Python applications. Adds support for Fast HTTP in Go. Adds support for Angular 20. Adds support for Next.js 15.x. Adds support for Go 1.26. Adds support for PyYAML in Python. Adds support for Apex 64 and Apex 65. Adds support for Spring Boot 4, Spring Core 7, and Spring Security 7 in Java. Adds support for the Svelte framework in JavaScript. Adds support for Ruby 4.0 and Rails 8.1. Adds taint propagation support for the Swift standard library on iOS. Adds support for the Go Fiber web framework. Adds support for AWS Glue in Python. Adds support for Semantic Kernel (SK) KernelContent and Taint Injection for .NET. Adds support for Azure Functions v4 on .NET 9 in isolated process mode. Adds support for .NET Semantic Kernel (SK) detection of hardcoded credentials (CWE-798) and configuration control issues (CWE-15). Adds support for PySpark, DynamoDB, and FastAPI in Python. Adds support for Semantic Kernel (SK) InvocationFilter and Filter for .NET. Adds support for JDK 25 (LTS). Adds initial support for iOS 26. Adds support for Go 1.25. Adds support for Micronaut 4.x in Java. Adds support for Node.js 22.x in JavaScript. Adds taint propagation support for Apple Platforms framework APIs. Adds taint sink coverage for System.Web.UI.Page.Title and System.Web.UI.HtmlControls.HtmlHead.Title in .NET for CWE-80 detection. Adds support for Dart 3.11 and Flutter 3.41. Adds support for Dart 3.10 and Flutter 3.38. Adds support for Dart 3.9 and Flutter 3.35. Adds support for Dart 3.8 and Flutter 3.32. Adds support for httplib in Python for detecting CWE-295 and CWE-297 flaws related to SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination. Adds support for os.path propagation in Python taint analysis. Expands third-party library detection to include Fluxnova in Java. Expands support for pnpm modules in JavaScript to improve dependency resolution. Enhances COBOL parsing to automatically detect copybooks.
Adds veracode.json support for excluding specific Java .jar files from static analysis.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Adds veracode.json support for excluding specific Java classes from Static Analysis. Adds .NET Semantic Kernel (SK) InvocationFilter and Filter support for .NET SAST. Adds support for the CloudKit framework for Apple Platforms. Adds support for Apple Security framework APIs.
+7 more
show less
Adds support for scanning Java source code. Adds support for viewing Java source code on the Veracode platform. Adds support for the Svelte framework in JavaScript. Adds support for Semantic Kernel (SK) KernelContent and Taint Injection for .NET. Adds support for Azure Functions v4 on .NET 9 in isolated process mode. Adds support for .NET Semantic Kernel (SK) detection of hardcoded credentials (CWE-798) and configuration control issues (CWE-15). Adds initial support for iOS 26.
46 more in Everything
CLI updates (2026-08-31)
Aug 31, 2026
·
issue 061
Veracode CLI gains toolchain discovery, new packaging flags, SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. OAuth2 OAuth2 An open authorization framework (RFC 6749) that lets a service grant limited access to a user's resources on another service without exposing credentials, giving cyber tools a standard way to authenticate against third-party APIs.
Adds --exclude flag to veracode package to prevent specified Java packages or JAR files from being scanned (v2.51.0). Adds --skip-packagers flag to veracode package to exclude specific artifacts (e.g. unsupported SQL) from packaging without affecting other languages (v2.48.0). Adds --java-source flag and VERACODE_PACKAGE_JAVA_SOURCE=true environment variable to veracode package for Java source code packaging (v2.46.0). Adds VERACODE_PACKAGE_GOLANG_GENERATE environment variable to enable client-side CGO code generation when packaging Go applications (v2.43.0). Adds SRCLR_MAKE_WINDOWS environment variable to enable preprocessing C/C++ source files with Make on Windows using a native Windows gcc or clang compiler (v2.44.0).
+28 more
show less
Introduces veracode package discover command to detect toolchains required to successfully create scannable artifacts (v2.44.0). veracode package discover adds toolchain detection for Java projects using Gradle (v2.46.0).veracode package discover adds toolchain detection for JavaScript projects using npm or Yarn (v2.52.0).veracode package discover introduces exit codes (v2.48.0).Introduces veracode auth login command for onboarding new users via OAuth2 (v2.41.0). veracode package introduces exit codes 5, 6, and 7 to improve CI/CD pipeline automation and error handling (v2.49.0).Adds --strict flag to veracode package: when enabled, returns exit code 4 for any build failures during packaging (v2.39.0). veracode dynamic scan now supports target UUIDs UUIDs A universally unique identifier, usually a 128-bit value used to identify an object across systems. It is designed to make independently generated identifiers unlikely to collide. veracode scan allows applying a custom policy defined in the Veracode Platform and enables viewing policy evaluation for individual findings alongside the overall policy result (v2.44.0).veracode scan introduces schema enhancements for container and IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. veracode scan categorizes secret-type findings as Critical in scan results (v2.45.0).veracode scan prioritizes vulnerability results from the NVD NVD The National Vulnerability Database, maintained by NIST, is the U.S. government repository of CVE records enriched with CVSS scores and metadata; cyber tools query it to drive vulnerability prioritization. veracode scan enables specifying a custom location for downloading vulnerability databases (v2.41.0).veracode scan adds Dockerfile heredoc syntax parsing support (v2.41.0).veracode sca command now supports SBOM generation via SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. CycloneDX 1.6 CycloneDX 1.6 An OWASP-maintained Software Bill of Materials standard that catalogs components, dependencies, and supply-chain metadata; tools use it to produce or consume machine-readable SBOMs in a widely supported schema. SPDX 2.3 SPDX 2.3 An open standard from the Linux Foundation for describing software bills of materials, letting cyber tools exchange dependency, license, and vulnerability data in a common machine-readable format. veracode package adds support for requirements-dev.txt in Python packaging workflows to include development dependencies (v2.48.0).veracode package supports the Poetry package management tool in Python for autopackaging (v2.47.0).veracode package adds support for generic packager for Apex (v2.43.0).veracode package supports Go v1.24 (v2.40.0).veracode package supports .NET 9 (v2.38.2).veracode package supports MSBuild .NET framework packaging (v2.42.0).veracode package adds support for preprocessor header files used to build PCH (v2.41.0).veracode package adds the option to process all Makefiles in a directory tree (v2.41.0).Preprocessed source code scanning is now the default method for C/C++ projects on Windows, and support is now available on Linux as well (v2.39.0). veracode static scan displays the Static Engine version in the scan summary (v2.42.0).veracode policy command now automatically determines and generates appropriate output artifacts based on the policy created (v2.50.0).veracode scan creates a separate asset for each repository in the ADO workflow for easier individual scan result tracking (v2.44.0).The SRCCLR_DOWNLOAD_URL environment variable now defaults to https://sca-downloads.veracode.com (v2.39.0).
33 details in Everything
└──▷ BREAKING ON UPGRADE
! The previous SRCCLR_DOWNLOAD_URL default of https://download.sourceclear.com is now deprecated; all instances in your environment should be updated to https://sca-downloads.veracode.com (v2.39.0).! Using old CLI versions (prior to v2.48.0) with the veracode scan command will result in incomplete data displayed in the Veracode Platform (v2.48.0).! The veracode static scan command no longer includes the --verbose flag by default (v2.38.2).
Veracode adds region switching in VS Code OAuth, custom predependency commands in GitHub Workflows, and Next.js 16.x / Android 16 static analysis support.
Adds support for custom predependency commands in the Veracode YAML file for the GitHub Workflow Integration v2.1.3, enabling project preparation steps before scanning. Adds a Current File filter to Static Scan Findings in Veracode Scan for VS Code v1.16.3, scoping displayed findings to the file open in the editor. Adds an option to filter and group Static Scan Findings by file name, with findings for each file grouped by severity, in VS Code v1.16.3. Adds an option to change the region during OAuth authentication in VS Code v1.16.3, with the current or most recently used region displayed on the OAuth screen. Static Analysis Engine v2026.08 adds support for Next.js 16.x.
+4 more
show less
Static Analysis Engine v2026.08 adds support for Android 16. Static Analysis Engine v2026.08 adds support for the Python google-cloud-bigquery library. Static Analysis Engine v2026.08 adds detection of hardcoded values in get assignments modeled as getter functions. Static Analysis Engine v2026.08 improves detection of hardcoded passwords and credentials associated with CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
9 details in Everything
Veracode Scan for VS Code v1.16.3 adds current file filter and OAuth region selection
└──▷ HOW TO FIND IT
Focus analysis on the file you are editing right now instead of scanning the entire project.
📍 In the Static Scan Findings panel, click the Current File filter checkbox to isolate findings for the active editor tab.
Ensure OAuth authentication uses the correct regional endpoint when connecting to Veracode services.
📍 On the OAuth authentication screen, locate the region selector below Authentication and choose your desired region from the dropdown.
Adds Current File filter to Static Scan Findings view in Veracode Scan for VS Code to show findings only for the open editor file Adds option to select OAuth authentication region on the auth screen, displaying the current or most recently used region below Authentication Adds ability to filter and group Static Scan Findings by file name with severity grouping
3 details in Everything
Veracode Scan for VS Code v1.16.3 adds region selection during OAuth and file-based filtering for static scan findings.
Current File filter in Static Scan Findings to view findings for the open editor fileFilter and group Static Scan Findings by file name, grouped by severity
2 details in Everything
Static Analysis Engine v2026.08 adds Dart getter detection, Next.js 16.x, Python google-cloud-bigquery support, and Android 16.
Adds get assignment detection for hardcoded values in Dart/Flutter projects Adds support for scanning Next.js 16.x applications
2 details in Everything
Veracode GitHub Workflow Integration v2.1.3 adds custom predependency commands to Veracode YAML
Integration updates (2026-08-24)
Aug 24, 2026
·
issue 056
Veracode integrations gain GitHub Platform install/scheduling, ADO agent pool config, scan scope selection, and expanded API wrapper capabilities.
└──▷ USE IT
Enable debug logging in a Veracode workflow integration to troubleshoot scan pipeline issues.
veracode.yml
copy
debug: true
Run scheduled scans against a specific analysis branch rather than the default branch in Azure DevOps.
veracode.yml
copy
analysis_branch: main-security-review
Adds a custom agent pool name parameter in veracode.yml for Azure DevOps Workflow Integration v2.4.3, letting you specify the agent pool used for pipeline execution. Adds analysis_branch support in veracode.yml for Azure DevOps Workflow Integration v2.3.10 so scheduled scans run against a specified branch instead of the default branch. Adds the debug configuration option in veracode.yml for the Azure DevOps Workflow Integration v2.3.6, GitHub Workflow Integration v1.0.6, and GitLab Workflow Integration v2.1.4 to enable debugging and troubleshooting. Adds page size support to the Platform Applications API (/appsec/v1/applications) in Java API Wrapper v26.3.19.0 to improve efficiency when retrieving large application lists. Introduces support for the Veracode Platform paginated Sandbox REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
+13 more
show less
Adds support for the Veracode Platform Findings REST API in Java API Wrapper v26.2.18.0 to access open and mitigated application findings. Implements a configurable retry mechanism for the Platform Applications API (appsec/v1/applications) in Java API Wrapper v26.2.18.0 to handle transient failures and timeouts. GitHub Workflow Integration v2.0.0 enables installing, configuring, and updating credentials for the Veracode GitHub Integration directly from the Veracode Platform, eliminating manual GitHub Marketplace steps. GitHub Workflow Integration v2.0.0 adds the ability to schedule Static Analysis, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. GitHub Workflow Integration v2.0.0 adds autopackaging support for Apex, VB6, and Perl. GitHub Workflow Integration v2.1.1 introduces a new uninstallation workflow on the Veracode Platform to uninstall the Veracode app from GitHub organizations. Adds a Scan Scope setting in Veracode Scan for Visual Studio v0.8.0 to scan either the full project directory or only the active solution for faster, more focused results. Adds usage analytics in Veracode Scan for Visual Studio v0.8.0 and Veracode Scan for JetBrains v1.8.0 and VS Code v1.16.0 to provide insights into plugin adoption, feature usage, and scan activity. Azure DevOps Workflow Integration v2.3.9 adds the ability to schedule scans for every organization where the integration is installed, based on configurations in veracode.yml. Veracode Azure DevOps extension v3.35.0 replaces the deprecated Veracode Flaw Importer task (with spaces) with the new VeracodeFlawImporter task for compatibility with a future Microsoft TFX packaging library upgrade. Veracode Scan for Visual Studio v0.7.2 adds support for Visual Studio 2026. GitHub Workflow Integration v2.1.1 updates the default runner image to scm-packaging-5.0.0, adding Alpine v3.24.0, Ubuntu v26.04, .NET v10, PipEnv v2026.6.2, libicu v78, Node.js v22.22.1, and Python v3.14.4. GitHub Veracode Workflow App permissions are downgraded to remove administration permissions, preventing the app from altering or removing repositories where it is installed.
18 details in Everything
└──▷ BREAKING ON UPGRADE
! The Veracode Flaw Importer task (with spaces in the task name) in the Veracode Azure DevOps extension is deprecated and scheduled for removal in a future release; replace it with VeracodeFlawImporter.! Support for the Veracode Integration for Jira on Jira Server and Jira Data Center 9.x ends November 30, 2026; upgrade to Jira 10 or later to continue using a supported version.
Veracode eLearning reports now support date ranges up to one year in the past.
Integration updates (2026-08-19)
Aug 19, 2026
·
issue 052
Veracode integrations gain GitHub/Azure DevOps platform-managed installs, scan scheduling, new veracode.yml keys, and expanded Java API Wrapper support.
└──▷ USE IT
Target scheduled Azure DevOps scans at a specific branch rather than the repo default, useful when your mainline integration branch differs from the default.
veracode.yml
copy
# veracode.yml
analysis_branch: main-security
Enable debug output in veracode.yml to troubleshoot pipeline scan failures across GitHub, GitLab, or Azure DevOps Workflow Integrations.
veracode.yml
copy
# veracode.yml
debug: true
Adds analysis_branch key support in veracode.yml for Azure DevOps Workflow Integration v2.3.10 so scheduled scans run against a specified branch instead of the default branch. Adds debug configuration option in veracode.yml for Azure DevOps Workflow Integration v2.3.6, GitHub Workflow Integration v1.0.6, and GitLab Workflow Integration v2.1.4 to enable debugging and troubleshooting. Adds custom agent pool name parameter in veracode.yml for Azure DevOps Workflow Integration v2.4.3 to specify the agent pool used for pipeline execution. Java API Wrapper v26.3.19.0 adds page size support to the Platform Applications API (/appsec/v1/applications) and introduces support for the paginated Sandbox REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Java API Wrapper v26.2.18.0 adds support for the Veracode Platform Findings REST API to access open and mitigated application findings, and implements a configurable retry mechanism for appsec/v1/applications.
+11 more
show less
GitHub Workflow Integration v2.0.0 enables installing, configuring, and updating credentials for the GitHub integration directly from the Veracode Platform, eliminating manual GitHub Marketplace steps. GitHub Workflow Integration v2.0.0 adds autopackaging support for Apex, VB6, and Perl. GitHub Workflow Integration v2.0.0 enables scheduling Static Analysis, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. GitHub Workflow Integration v2.1.1 adds a new uninstallation workflow on the Veracode Platform to uninstall the Veracode app from GitHub organizations. Azure DevOps Workflow Integration v2.3.9 enables scheduling scans for every organization where the integration is installed, driven by veracode.yml configuration. Azure DevOps Workflow Integration v2.3.3 enforces SCA scan failure when vulnerabilities are found under a custom policy with the Build Action: error configuration for agent-based scans. Veracode Scan for Visual Studio v0.8.0 adds a Scan Scope setting to choose between scanning the full project directory or only the active solution. Veracode Scan for Visual Studio v0.8.0 and Veracode Scan for JetBrains v1.8.0 add usage analytics for plugin adoption, feature usage, and scan activity. Veracode Scan for VS Code v1.16.0 adds usage analytics for plugin adoption, feature usage, and scan activity. GitHub Workflow Integration v2.1.1 updates the default runner image to scm-packaging-5.0.0, including Alpine v3.24.0, Ubuntu v26.04, .NET v10, PipEnv v2026.6.2, libicu v78, Node.js v22.22.1, and Python v3.14.4. GitHub Veracode Workflow App permissions are downgraded to remove administration permissions, preventing the app from altering or removing installed repositories.
16 details in Everything
└──▷ BREAKING ON UPGRADE
! The Veracode Flaw Importer task (with spaces in the task name) in the Veracode Azure DevOps extension v3.35.0 is deprecated and replaced by VeracodeFlawImporter; the old task is scheduled for removal in a future release.! Veracode will end support for the Veracode Integration for Jira on Jira Server and Jira Data Center 9.x on November 30, 2026; upgrade to Jira 10 or later to maintain a supported configuration.
Adds custom agent pool configuration to Veracode Azure DevOps integration.
└──▷ USE IT
Direct Veracode pipeline execution to a specific Azure DevOps agent pool by adding the agent_pool key to your veracode.yml configuration file.
yaml
copy
# Example veracode.yml snippet
task: scan
project_name: "My App"
agent_pool: "custom-pool-name"
Allows specifying a custom agent pool name via agent_pool parameter in veracode.yml.
1 detail in Everything
Veracode adds business unit selection for DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Adds business unit selection when creating a web application or API specification target, or on the DAST configuration page. Adds real-time in-app notifications when scans complete, fail, or are cancelled. Adds improved detection for CAA record checks on SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination. CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
3 details in Everything
Integration updates (2026-08-10)
Aug 10, 2026
·
issue 042
Veracode integrations gain GitHub/ADO platform-managed installs, scan scheduling, autopackaging for Apex/VB6/Perl, and new Java API Wrapper endpoints.
└──▷ USE IT
Target a specific branch for scheduled scans in an ADO workflow instead of the default branch.
yaml
copy
# veracode.yml
analysis_branch: main-release
Enable debug output in a veracode.yml-driven workflow (GitHub, GitLab, or ADO) to troubleshoot scan pipeline issues.
yaml
copy
# veracode.yml
debug: true
Adds analysis_branch key to veracode.yml in the Azure DevOps Workflow Integration v2.3.10: scheduled scans now run against the specified branch instead of the default branch. Adds debug configuration option to veracode.yml across Azure DevOps Workflow Integration v2.3.6, GitHub Workflow Integration v1.0.6, and GitLab Workflow Integration v2.1.4 for debugging and troubleshooting. Adds page size support to the Platform Applications API (/appsec/v1/applications) in Java API Wrapper v26.3.19.0 to improve efficiency when retrieving large application lists. Adds support for the Veracode Platform paginated Sandbox REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Adds support for the Veracode Platform Findings REST API in Java API Wrapper v26.2.18.0 to access open and mitigated application findings.
+13 more
show less
Implements a configurable retry mechanism for the Platform Applications API (appsec/v1/applications) in Java API Wrapper v26.2.18.0 to handle transient failures and timeouts. GitHub Workflow Integration v2.0.0 enables installing, configuring, and updating credentials for the Veracode GitHub Integration directly from the Veracode Platform, removing the requirement for manual GitHub Marketplace steps. GitHub Workflow Integration v2.0.0 adds scan scheduling for Static Analysis, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. GitHub Workflow Integration v2.0.0 adds autopackaging support for Apex, VB6, and Perl. GitHub Workflow Integration v2.1.1 ships an updated default runner image scm-packaging-5.0.0 with Alpine v3.24.0, Ubuntu v26.04, .NET v10, PipEnv v2026.6.2, libicu v78, Node.js v22.22.1, and Python v3.14.4. GitHub Workflow Integration v2.1.1 adds a new uninstallation workflow accessible from the Veracode Platform to remove the Veracode app from GitHub organizations. Azure DevOps Workflow Integration v2.3.9 adds the ability to schedule scans for every organization where the integration is installed, driven by veracode.yml configuration. Veracode Scan for Visual Studio v0.8.0 adds a Scan Scope setting to choose between scanning the full project directory or only the active solution. Veracode Scan for Visual Studio v0.8.0 adds usage analytics providing insights into plugin adoption, feature usage, and scan activity. Veracode Scan for Visual Studio v0.7.2 adds support for Visual Studio 2026. Azure DevOps Workflow Integration v2.3.3 enforces Build Action: error custom policy behavior for SCA agent-based scans, causing the scan to fail when vulnerabilities are found. The VeracodeFlawImporter task replaces the deprecated Veracode Flaw Importer task (space-separated name) in Veracode Azure DevOps extension v3.35.0; both are currently supported. Reduces GitHub Veracode Workflow App permissions by removing administration access, preventing the app from altering or removing installed repositories.
18 details in Everything
└──▷ BREAKING ON UPGRADE
! The Veracode Flaw Importer task (with spaces) in the Veracode Azure DevOps extension is deprecated and scheduled for removal in a future release; replace it with VeracodeFlawImporter.! Support for the Veracode Integration for Jira on Jira Server and Jira Data Center 9.x ends November 30, 2026; upgrade to Jira 10 or later to maintain a supported configuration.
DAST updates (2026-08-06)
Aug 6, 2026
·
issue 038
Veracode DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Adds custom host-to-IP address mapping configuration for DAST scans when DNS lookup is unavailable or not desired. Adds Directory Restrictions to target configuration to control DAST scan scope. Enhances the DAST Schedule feature with advanced scheduling capabilities and greater configuration flexibility; all existing schedules are automatically migrated. Enables selection of a business unit when creating a web application or API specification target, or on the DAST configuration page. Adds improved detection for CAA record checks on SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination. CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
+15 more
show less
Dynamic Analysis and DAST Enterprise Mode now support scanning web applications for open ports. Adds new detections for HTTP headers, TLS, and fingerprinting to the scan engine. DAST Enterprise mode now supports downloadable scan reports providing visibility into scan coverage and scanner behavior. DAST Enterprise mode now provides AI-assisted login, an AI-based authentication method that handles complex login flows without requiring recorded login scripts. EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do. DAST now supports manual application linking to the Veracode Platform for policy evaluation and combined multi-scan-type reporting. The DAST Target Configuration Service REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. API scanning now supports uploading and scanning Postman Collections. Web application and API scans now support time-based one-time password (TOTP TOTP A one-time password algorithm (RFC 6238) that generates short-lived codes from a shared secret and the current time, giving cyber tools phishing-resistant second-factor authentication without a server round-trip. MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. Web application and API scans now support one or more custom cookies for authentication. ISM endpoint 24.10.0 introduces a proxy exclusion list for hosts that should bypass configured proxy settings. DAST Enterprise mode adds support for login scripts, scanner variables, client certificates for web applications, and Scriptable Request Modifications (SRM) for APIs. DAST Enterprise mode adds support for uploading or dynamically referencing API specifications and enables Internal Scanning Management (ISM) for scanning behind a corporate firewall. Adds ability to schedule an analysis to pause and resume on specific days of the week, during specific periods, or both. Dynamic Analysis REST API now supports setting URL scan settings at the organization level for all analyses and scans.
20 details in Everything
└──▷ BREAKING ON UPGRADE
! The DAST scheduling REST API endpoints have changed; integrations that use the REST API to manage schedules must be updated to use the new endpoints (refer to the DAST API specification for details).
Training updates (2026-08-06)
Aug 6, 2026
·
issue 037
Veracode training adds LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code. OWASP Top 10:2025 OWASP Top 10:2025 A ranked list of the ten most critical web application risk categories, maintained by the Open Worldwide Application Security Project, used by cyber tools to prioritize detection, testing, and remediation coverage. updatedAfter and excludeNotStarted parameters.
Adds updatedAfter parameter to the Get Lesson Progress API to support incremental loads of lesson progress data. Adds excludeNotStarted=true parameter to the Get Lesson Progress API to filter out lessons that have not been started. Get Lesson Progress API now includes stack and updated_on fields in the response, and surfaces Not Started status when both start_time and end_time are null. Adds Security Labs team search capability for Security Labs administrators and managers. Integrates Security Labs user and team management into the Veracode Platform via Veracode IAM IAM Identity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access.
+9 more
show less
Changes the default Security Labs URL from https://securitylabs.veracode.com/ to https://securitylabs.veracode.com/security-labs/. New OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. New eLearning courses aligned to OWASP Top 10:2025 available in English, Spanish, French, Portuguese, and Chinese: Software Security Awareness, Secure coding for .NET, Java, JavaScript, PHP, and Python. New Container Security in Docker Security Labs lesson series covering capabilities, users, virtualization, networking, resources, and inventory across dozens of hands-on lessons. New eLearning assessment quiz courses (skills assessments) available in English, Portuguese, and Spanish for Static Analysis, Dynamic Analysis, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. Adds CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. CWEs CWEs A community-maintained list of software and hardware weakness types, maintained by MITRE, that gives cyber tools a standard taxonomy for classifying and communicating vulnerability root causes. Adds code syntax highlighting to Security Labs lessons, tailored per programming language. Upgrades OWASP API Security Top 10 coverage in Security Labs from the 2019 list to the 2023 list, adding lessons for three new categories. New in-app guidance available in Security Labs for creating campaigns and using reporting (requires third-party cookies enabled in Chrome, Edge, Firefox, Safari, and Internet Explorer 9+).
14 details in Everything
└──▷ BREAKING ON UPGRADE
! The default Security Labs URL has changed from https://securitylabs.veracode.com/ to https://securitylabs.veracode.com/security-labs/; customers using SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. ! In Security Labs, Teams are now called Organizations and Roles are now called Teams ; any documentation, automation, or integrations referencing these terms must be updated.! The Security Labs community edition will be deprecated on July 31, 2026.! 33 deprecated eLearning courses (OWASP 2017, OWASP Top 10 2021, and language-specific Secure Coding courses for .NET, Java, JavaScript, PHP, and Python) are no longer available as of June 10, 2026.! OWASP Top 10 (2021) Security Labs lessons are no longer available as of June 10, 2026.
Veracode adds business unit selection during web app/API target creation and DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces. CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
└──▷ HOW TO FIND IT
Select a specific business unit when defining a new API specification target to ensure proper asset grouping.
📍 In the console, go to Targets › API Specifications and select your business unit during creation
Assign a business unit while configuring a new DAST scan scope.
📍 In the console, go to DAST configuration and select your business unit from the dropdown
Adds the ability to select a business unit when creating a web application or API specification target Adds the ability to select a business unit on the DAST configuration page Improves detection for CAA record checks on SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination.
3 details in Everything
Business unit and scan engine enhancements
Aug 6, 2026
· release notes
Adds business unit selection during target creation/DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces. SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination.
Allows selecting a business unit when creating a web application or API specification target, or on the DAST configuration page.
1 detail in Everything
EASM updates (2026-08-05)
Aug 5, 2026
·
issue 037
Veracode EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do. DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Adds real-time in-app notifications when scans complete, fail, or are cancelled. Adds multi-project visibility for centralized risk management across all projects. Adds scan scheduling to streamline scan orchestration across projects. Adds AI-powered intelligence for accelerated risk prioritization. Adds a Findings view with improved prioritization workflows and expanded reporting capabilities.
+5 more
show less
Adds Issues capability to streamline remediation efforts and improve cyber hygiene focus. Enables export of web applications from EASM directly into DAST Essentials by marking assets as DAST Candidates. Adds Dashboard Heatmap, World map, and Things widgets with filterable data views and a shortcut to create reports. Adds business units management: create, assign, and manage business units with domain associations. Enhances Deep Discovery with an improved work queue, selection toggles, and clearer result indicators.
10 details in Everything
Veracode adds a Custom PDF REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
New Custom PDF REST API enables programmatic generation of custom PDF reports. Pipeline Scan now supports packaged artifacts larger than 200 MB with no changes to existing integrations required. New uninstallation workflow on the Veracode Platform lets you uninstall the Veracode app from GitHub organizations. Veracode CLI v2.51.2 adds enhanced batch fix processing, enabling remediation of a large number of vulnerabilities in a single batch operation. Veracode CLI v2.51.2 improves policy enforcement to ensure vulnerability severity thresholds are consistently applied.
+1 more
show less
GitHub Workflow Integration v2.1.1 updates the default runner image to scm-packaging-5.0.0, adding Alpine v3.24.0, Ubuntu v26.04, .NET v10, PipEnv v2026.6.2, libicu v78, Node.js v22.22.1, and Python v3.14.4.
6 details in Everything
CLI updates (2026-07-31)
Jul 31, 2026
·
issue 052
Veracode CLI gains batch fix processing, --exclude and --skip-packagers flags, target UUID UUID A universally unique identifier, usually a 128-bit value used to identify an object across systems. It is designed to make independently generated identifiers unlikely to collide.
Adds --exclude flag to veracode package to prevent specified Java packages or JAR files from being scanned (v2.51.0). Adds --skip-packagers flag to veracode package to exclude specific artifacts (e.g. unsupported SQL) from packaging results without affecting other languages (v2.48.0). Adds --java-source flag and VERACODE_PACKAGE_JAVA_SOURCE=true environment variable to veracode package for Java source code packaging (v2.46.0). Adds VERACODE_PACKAGE_GOLANG_GENERATE environment variable to veracode package to enable client-side CGO code generation when packaging Go applications (v2.43.0). Adds SRCLR_MAKE_WINDOWS environment variable to enable preprocessing C/C++ source files with Make on Windows using a native Windows gcc or clang compiler (v2.44.0).
+28 more
show less
Introduces exit codes 5, 6, and 7 to veracode package to improve CI/CD automation and error handling for packaging or build issues (v2.49.0). Introduces exit codes to the veracode package discover command (v2.48.0). Adds a new optional --strict flag to veracode package: when enabled, the CLI returns exit code 4 for any build failures during packaging (v2.39.0). Introduces the veracode package discover command to detect toolchains required to successfully create scannable artifacts (v2.44.0). Adds toolchain detection for Java projects using the Gradle package manager to veracode package discover (v2.46.0). veracode fix now supports enhanced batch fix processing enabling remediation of a large number of vulnerabilities in a single batch operation (v2.51.2).veracode dynamic scan now supports target UUIDs UUIDs A universally unique identifier, usually a 128-bit value used to identify an object across systems. It is designed to make independently generated identifiers unlikely to collide. veracode scan now allows applying a custom policy defined in the Veracode Platform and viewing policy evaluation for individual findings alongside the overall policy result (v2.44.0).veracode scan categorizes secret-type findings as Critical in scan results (v2.45.0).veracode scan prioritizes vulnerability results from the NVD NVD The National Vulnerability Database, maintained by NIST, is the U.S. government repository of CVE records enriched with CVSS scores and metadata; cyber tools query it to drive vulnerability prioritization. veracode scan introduces schema enhancements for container and IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Introduces the auth login command to onboard new users via OAuth2 OAuth2 An open authorization framework (RFC 6749) that lets a service grant limited access to a user's resources on another service without exposing credentials, giving cyber tools a standard way to authenticate against third-party APIs. veracode sca now supports SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. CycloneDX 1.6 CycloneDX 1.6 An OWASP-maintained Software Bill of Materials standard that catalogs components, dependencies, and supply-chain metadata; tools use it to produce or consume machine-readable SBOMs in a widely supported schema. SPDX 2.3 SPDX 2.3 An open standard from the Linux Foundation for describing software bills of materials, letting cyber tools exchange dependency, license, and vulnerability data in a common machine-readable format. veracode scan enables specifying a custom location from which vulnerability databases can be downloaded (v2.41.0).veracode scan adds support for parsing Dockerfile heredoc syntaxes (v2.41.0).veracode package adds support for the Poetry package management tool in Python for autopackaging (v2.47.0).veracode package adds support for requirements-dev.txt in Python packaging workflows to include development dependencies (v2.48.0).veracode package supports generic packager for Apex (v2.43.0).veracode package adds support for packaging MSBuild .NET framework (v2.42.0).veracode package adds support for Go v1.24 (v2.40.0).veracode package adds support for .NET 9 (v2.38.2).Preprocessed source code scanning is now the default method for C/C++ projects on Windows, and support is now available on Linux replacing the previous autopackaging solution (v2.39.0). Adds --verbose flag to veracode package; the --debug flag is deprecated but still available (v2.38.0). All Veracode CLI commands can consistently read access tokens access tokens A credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions. SRCCLR_DOWNLOAD_URL environment variable now defaults to https://sca-downloads.veracode.com (v2.39.0).veracode package adds the option to process all Makefiles in a directory tree (v2.41.0).veracode package adds the ability to include directory path in the artifact name to make flaws easier to locate (v2.41.0).veracode static scan now retries failed scans up to five times on server errors or too-many-requests responses (v2.38.0).
33 details in Everything
└──▷ BREAKING ON UPGRADE
! The veracode static scan command no longer includes the --verbose flag by default (v2.38.2).! The --debug flag on veracode package is deprecated in favor of --verbose (v2.38.0).! The previous SRCCLR_DOWNLOAD_URL default of https://download.sourceclear.com is now deprecated; the new default is https://sca-downloads.veracode.com — update all instances in your environment (v2.39.0).! Using old CLI versions (pre-v2.48.0) with the Veracode Platform will result in incomplete data displayed in the platform (v2.48.0).
Integration updates (2026-07-30)
Jul 30, 2026
·
issue 030
Veracode integrations gain platform-driven GitHub install/uninstall, scheduled scans, new API pagination, and broader language autopackaging support.
└──▷ USE IT
Enable debug logging for a GitHub or Azure DevOps workflow scan to troubleshoot packaging or scan failures.
yaml
copy
# In veracode.yml
debug: true
Install and schedule Veracode GitHub Integration scans from the platform without touching the GitHub Marketplace.
📍 In the Veracode Platform, go to Integrations › GitHub › Install, select your organization, configure credentials, then go to Schedule Scans to set up Static Analysis, SCA, or IaC scan schedules.
Scope a Visual Studio scan to only the active solution for faster, more focused results in large repos.
📍 In Visual Studio with the Veracode Scan extension, open Settings › Veracode Scan and set Scan Scope to Active Solution , then run a scan.
Adds a new uninstallation workflow on the Veracode Platform to remove the Veracode app from GitHub organizations. Enables installing, configuring, and updating credentials for the Veracode GitHub Integration directly from the Veracode Platform, bypassing manual GitHub Marketplace steps. Adds autopackaging support for Apex, VB6, and Perl in the GitHub Workflow Integration. Enables scheduling Static Analysis, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Adds scheduled scan support for every organization where the Azure DevOps Workflow Integration is installed, driven by veracode.yml configuration.
+14 more
show less
Adds a Scan Scope setting in Veracode Scan for Visual Studio to scan the full project directory or only the active solution. Adds Visual Studio 2026 support in Veracode Scan for Visual Studio. Adds page size support to the Platform Applications API (/appsec/v1/applications) in the Java API Wrapper for efficient large-list retrieval. Introduces support for the Veracode Platform paginated Sandbox REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Adds support for the Veracode Platform Findings REST API in the Java API Wrapper to access open and mitigated application findings. Adds a configurable retry mechanism for the Veracode Platform Applications API in the Java API Wrapper. Adds a debug configuration option in veracode.yml for the Azure DevOps Workflow Integration, GitHub Workflow Integration, and GitLab Workflow Integration for debugging and troubleshooting. Adds support for Windows-based runners in the GitHub Workflow Integration. Enforces custom platform policies with Build Action: error for SCA agent-based scans in the Azure DevOps Workflow Integration, failing the scan when vulnerabilities are found. Imports static scan results from the Veracode Platform directly into the Visual Studio IDE. Proposes mitigations for static scan flaws directly within the Visual Studio IDE. Ensures findings marked as mitigated on the platform are excluded from Azure DevOps pipeline scan results. Adds usage analytics in Veracode Scan for JetBrains, VS Code, and Visual Studio for insights into plugin adoption, feature usage, and scan activity. Scheduled scans in the Azure DevOps Workflow Integration now run against the analysis_branch specified in veracode.yml instead of the default branch.
19 details in Everything
└──▷ BREAKING ON UPGRADE
! The Veracode Flaw Importer task (with spaces in the task name) in the Azure DevOps extension is deprecated and replaced by VeracodeFlawImporter; the old task is scheduled for removal in a future release.
New GitHub app uninstall workflow; optimized Jira flaw import in v4.17.x; updated runner image in GitHub integration v2.1.1.
Adds a new uninstallation workflow to remove the Veracode app from GitHub organizations via the Veracode Platform UI Improves scheduled flaw import performance in Veracode Integration for Jira Server v4.17.0 and v4.17.1 by optimizing application lookup operations Updates the default runner image for the GitHub Workflow Integration to scm-packaging-5.0.0, including Alpine v3.24.0, Ubuntu v26.04, .NET v10, PipEnv v2026.6.2, libicu v78, Node.js v22.22.1, and Python v3.14.4
3 details in Everything
└──▷ BREAKING ON UPGRADE
! Support for Jira Server and Jira Data Center 9.x ends on November 30, 2026 for the Veracode Integration for Jira; users must upgrade to Jira 10 or later
Platform updates (2026-07-29)
Jul 29, 2026
·
issue 030
Veracode adds Custom PDF REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. XML APIs XML APIs Interfaces for reading, writing, or querying XML documents, provided by libraries such as libxml2 or built into language runtimes; cyber tools use them to parse structured data like configs, reports, or protocol messages reliably.
New Custom PDF REST API enables programmatic generation of custom PDF reports. XML APIs now support OAuth Client Credentials authentication, in addition to REST APIs REST APIs A convention for building HTTP-based interfaces where resources are addressed by URL and manipulated with standard verbs like GET, POST, and DELETE, giving cyber tools a predictable way to integrate with external services. Auto-Update OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. OWASP Top 10:2025 OWASP Top 10:2025 A ranked list of the ten most critical web application risk categories, maintained by the Open Worldwide Application Security Project, used by cyber tools to prioritize detection, testing, and remediation coverage. MITRE MITRE A US federally funded research and development center that maintains public frameworks—ATT&CK, CVE, D3FEND—that cyber tools use to classify threats, vulnerabilities, and defensive techniques in a common language. Six new built-in security policies added to the Veracode Platform. Veracode Analytics upgraded to Looker 26.6 with finer widget sizing, persistent filtering, and tabbed dashboards.
+18 more
show less
Finding Reporting API responses now include a collections_list field returning collection names associated with an application. Veracode Analytics Applications explore now includes Collections fields, and the Policy Compliance Overview dashboard adds Collections visualizations. Reporting API Scans report supports new most_recent_scan filter to return only the most recent scan per asset. OAuth 2.0 OAuth 2.0 An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms. New Firewall Usage Dashboard and Explore in Veracode Analytics surface metrics for Veracode Firewall. Policy Settings page now supports light and dark mode. New library_instance_ref field added to Reporting API findings responses to uniquely identify specific library instances. Reporting API Findings report supports new custom_severity filter. New data_refresh_date field added to Reporting API metadata indicating the most recent Analytics data refresh time. Manual Penetration Testing (MPT) Flaw Matching correlates findings across tests for consistent flaw IDs, status values, and grace period inclusion. Administrators can now disable Veracode-defined roles for users who use custom roles, via the Platform UI and updated Identity API. Container and IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. New action_type filter available in the Reporting API Audit Log report for narrowing records by specific user actions. Reporting REST API now supports generating an Audit Log report for querying detailed user activity. Multiple domains can now be mapped to a single identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. SP-initiated SP-initiated A SAML or OAuth/OIDC login flow where the Service Provider redirects the user to an Identity Provider to authenticate, rather than the IdP pushing an assertion unprompted; tools use it to trigger SSO from their own login page. SAML SSO SAML SSO An authentication protocol that lets a user log in once with an identity provider and access multiple services without re-entering credentials, by passing signed XML assertions between parties. Customizable PDF reports now display SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. Administrators can now customize columns in the All Users table on the Administration page. Customer Managed Encryption Keys (CMEK) allows encryption of Veracode Platform data using an organization's own root encryption key, with KMS KMS A managed service that creates, stores, rotates and controls access to encryption keys, usually backed by HSMs. Applications ask it to encrypt or decrypt rather than holding keys themselves.
23 details in Everything
└──▷ BREAKING ON UPGRADE
! The Veracode Healthcheck endpoint /healthcheck/status has been removed and now returns a 404 error; use the v2/principal endpoint in the Identity REST API instead.
Static Analysis updates (2026-07-29)
Jul 29, 2026
·
issue 030
Veracode SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment.
Pipeline Scan now supports packaged artifacts larger than 200 MB with no integration changes required. Pipeline Scan results.json now includes a numeric exploit level (-2 to 2) for each finding, surfacing exploitability likelihood alongside vulnerability data. Static Analysis Engine v2026.07 adds support for Android 17 and enhances .NET 10 support. Static Analysis Engine v2026.07 expands JavaScript dependency resolution with pnpm module support. Static Analysis Engine v2026.07 expands third-party library detection in Java to include Fluxnova.
+33 more
show less
Static Analysis Engine v2026.06 adds support for Dart 3.12, Flutter 3.44, and Kotlin 2.4. Static Analysis Engine v2026.05 adds CloudKit and Apple Security framework API support for Apple platforms. Static Analysis Engine v2026.05 enhances JDK 25 support for Java. Static Analysis Engine v2026.04 adds support for scanning and viewing Java source code on the platform. Static Analysis Engine v2026.04 adds support for excluding Java .jar files from static analysis via veracode.json. Static Analysis Engine v2026.04 expands hardcoded secrets detection to include application configuration files with -local and -prod naming patterns. Static Analysis Engine v2026.04 adds support for React 19, Kotlin 2.3, Psycopg 3 (Python), and Xcode 26.4. Static Analysis Engine v2026.04 adds support for JDK 26. Static Analysis Engine v2026.03 adds support for Fast HTTP in Go, Angular 20, and Next.js 15.x. Static Analysis Engine v2026.03 skips @isTest methods in Apex scans to reduce noise. Static Analysis Engine v2026.02 adds support for Go 1.26 and PyYAML in Python. Static Analysis Engine v2026.02 adds support for excluding specific Java classes from Static Analysis via veracode.json. Static Analysis Engine v2026.01 adds support for Spring Boot 4, Spring Core 7, and Spring Security 7. Static Analysis Engine v2026.01 adds support for the Svelte framework in JavaScript. Static Analysis Engine v2026.01 adds support for Ruby 4.0 and Rails 8.1. Static Analysis Engine v2026.01 adds support for Apex 64 and Apex 65. Static Analysis Engine v2025.12 adds support for .NET 10, Dart 3.10, Flutter 3.38, and the Go Fiber web framework. Static Analysis Engine v2025.12 adds taint propagation support for the Swift standard library on iOS. Static Analysis Engine v2025.11 adds AWS Glue support for Python scanning. Static Analysis Engine v2025.10 adds support for .NET Semantic Kernel KernelContent and Taint Injection. Static Analysis Engine v2025.10 adds PySpark, DynamoDB, and FastAPI support for Python scanning. Static Analysis Engine v2025.10 enhances COBOL parsing with automatic copybook detection. Static Analysis Engine v2025.10 skips ProGuard-obfuscated Android classes to improve scan performance. Static Analysis Engine v2025.09 adds support for .NET Semantic Kernel InvocationFilter and Filter. Static Analysis Engine v2025.09 adds support for Dart 3.9, Flutter 3.35, and JDK 25 (LTS). Static Analysis Engine v2025.09 updates Gen IR: the --capture flag now includes diagnostic data in .xcarchive files. Adds initial support for iOS 26 in static analysis. Static Analysis Engine v2025.08 adds .NET Semantic Kernel support for detecting CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. Static Analysis Engine v2025.08 adds support for Azure Functions v4 on .NET 9 in isolated process mode. Static Analysis Engine v2025.08 adds support for Go 1.25, Node.js 22.x, Scala 3.7, Dart 3.8, and Flutter 3.32. Static Analysis Engine v2025.08 adds support for Micronaut 4.x and improves Quarkus support for Java. Introduces initial support for Android 16. Adds support for Apex 63 and improves detection of SOSL FIND queries.
38 details in Everything
Veracode adds CLI --exclude flag, DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
└──▷ TRY IT
Exclude a legacy JAR or noisy internal package from a Java scan to focus results on application code you own.
copy
$ veracode package --exclude com.example.legacy:legacy-lib.jar Configure a custom host-to-IP mapping for a DAST scan targeting an internal staging environment not resolvable via public DNS.
📍 In the Veracode Platform, open your DAST scan configuration, navigate to the Custom Host settings, and add a host-to-IP address mapping for your target host.
Adds --exclude flag to Veracode CLI v2.51.1 to prevent specified Java packages or JAR files from being scanned. Enables custom host-to-IP address mappings for DAST scans when DNS lookup is unavailable or not desired. Enhances Python static scanner with taint tracking, cross-file analysis, and pattern recognition; adds framework support for PySpark, Flask, Django, and FastAPI. Adds support for Android 17 in the Static Analysis Engine v2026.07. Enhances support for .NET 10 in the Static Analysis Engine v2026.07.
+4 more
show less
Expands third-party library detection to include Fluxnova. Expands support for pnpm modules to improve dependency resolution in static analysis. Improves JSP and JSF Expression Language modeling with more complete POJO data, potentially surfacing previously undetected findings. Enhances SQL dialect packaging support in Veracode CLI v2.51.1.
9 details in Everything
Veracode adds CLI --exclude flag, DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
└──▷ TRY IT
Exclude a legacy JAR or noisy internal package from a Java scan to focus results on application code you own.
copy
$ veracode package --exclude com.example.legacy:legacy-lib.jar Configure a custom host-to-IP mapping for a DAST scan targeting an internal staging environment not resolvable via public DNS.
📍 In the Veracode Platform, open your DAST scan configuration, navigate to the Custom Host settings, and add a host-to-IP address mapping for your target host.
Adds --exclude flag to Veracode CLI v2.51.1 to prevent specified Java packages or JAR files from being scanned. Enables custom host-to-IP address mappings for DAST scans when DNS lookup is unavailable or not desired. Enhances Python static scanner with taint tracking, cross-file analysis, and pattern recognition; adds framework support for PySpark, Flask, Django, and FastAPI. Adds support for Android 17 in the Static Analysis Engine v2026.07. Enhances support for .NET 10 in the Static Analysis Engine v2026.07.
+4 more
show less
Expands third-party library detection to include Fluxnova. Expands support for pnpm modules to improve dependency resolution in static analysis. Improves JSP and JSF Expression Language modeling with more complete POJO data, potentially surfacing previously undetected findings. Enhances SQL dialect packaging support in Veracode CLI v2.51.1.
9 details in Everything
SCA updates (2026-07-24)
Jul 24, 2026
·
issue 024
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue.
└──▷ TRY IT
Capture structured JSON scan output for automation while keeping a readable summary visible in the terminal during a CI run.
copy
$ srcclr scan . --json=results.json --show-cli Assign a Unified Policy to an SCA workspace so builds break based on policy criteria — navigate to the workspace policy settings in the Veracode Platform.
📍 In the Veracode Platform, go to SCA › Workspaces › <your workspace> › Policies, then select Assign Policy and choose or set a default Unified Policy.
Adds --appname flag to the SCA agent scan command (Commercial region) to link scan results directly to an application profile, requiring OAuth or HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it. Adds --show-cli flag to the SCA agent scan command: used with --json, it saves structured JSON output to a file while also displaying a human-readable summary in the console. Enables Unified Policy assignment to SCA agent-based scan workspaces in the US Federal region, allowing policies to create issues and break builds based on defined criteria. Enables Unified Policy assignment to SCA agent-based scan workspaces in the European region. Adds ability to configure the Vulnerability Severity policy rule (Commercial region) to break builds only when an upgrade path to fix a vulnerable component is available.
+14 more
show less
Adds malicious package detection to SCA upload and agent-based scans — no configuration or agent update required to enable. Adds support for generating SBOM files during SCA agent-based scans. Adds support for scanning SBOM files as part of SCA upload scans. Adds support for scanning SBOM files as part of SCA agent-based scans. Adds support for Python's Poetry package manager in SCA Upload scans. Adds support for Python's Poetry package manager in SCA agent-based scans. Adds support for Python 3.12 environments in SCA agent-based scans. Adds autopackaging support to the SCA agent (v3.8.114+), enabling automated packaging workflows without affecting existing scans. Adds deep link support for SCA pages: unauthenticated users are redirected to login and then back to the original scan results link. Adds vulnerability details side pane on the Vulnerabilities tab of the new SCA homepage (Beta). Updated digital certificate for the SCA agent enables customers to verify source and integrity of the agent file before execution. Changes default SCA agent download URL to https://sca-downloads.veracode.com (legacy https://download.sourceclear.com available for 12 more months). Changes default backend API URL for Commercial region customers to https://sca-api.veracode.com (legacy https://api.sourceclear.io available for 12 more months). Changes default backend API URLs for European and US Federal region customers to https://sca-api.veracode.eu and https://sca-api.veracode.us respectively.
19 details in Everything
└──▷ BREAKING ON UPGRADE
! The default SCA agent download URL changes from https://download.sourceclear.com to https://sca-downloads.veracode.com; the legacy URL will be retired after 12 months.! The default backend API URL for Commercial region customers changes from https://api.sourceclear.io to https://sca-api.veracode.com; the legacy URL will be retired after 12 months.! The default backend API URLs for European region customers change from https://platform-backend.analysiscenter.veracode.eu to https://sca-api.veracode.eu; legacy URLs will be retired after 12 months.! The default backend API URLs for US Federal region customers change from https://platform-backend.analysiscenter.veracode.us to https://sca-api.veracode.us; legacy URLs will be retired after 12 months.
DAST updates (2026-07-22)
Jul 22, 2026
·
issue 023
Veracode DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Adds custom host-to-IP address mapping configuration for DAST scans when DNS lookup is unavailable or not desired. Adds Directory Restrictions in DAST target configuration to control scan scope. Enhances DAST Schedule feature with advanced scheduling capabilities and greater configuration flexibility; all existing schedules are automatically migrated. Adds open-port scanning support for web applications in Dynamic Analysis and DAST Enterprise mode. Adds new detections for HTTP headers, TLS, and fingerprinting to the DAST scan engine.
5 details in Everything
└──▷ BREAKING ON UPGRADE
! The DAST REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Static Analysis updates (2026-07-22)
Jul 22, 2026
·
issue 023
Veracode SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment.
└──▷ USE IT
Exclude a bundled third-party .jar from static analysis to eliminate noise from non-application code.
json
copy
{
  "exclude": [
    "lib/third-party-sdk.jar"
  ]
}
Exclude a specific Java class (e.g., generated code) from Static Analysis results via veracode.json.
json
copy
{
  "exclude": [
    "com/example/generated/AutoGeneratedClient.class"
  ]
}
Adds enhanced Python scanner with improved taint tracking, cross-file analysis, and pattern recognition — applies automatically to all Python scans from July 22, 2026. Adds Python framework support for PySpark, Flask, Django, and FastAPI in the enhanced scanner. Adds Python support for httplib to detect CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination. Adds support for Dart 3.12 and Flutter 3.44 in v2026.06. Adds support for Kotlin 2.4 in v2026.06.
+23 more
show less
Adds support for the CloudKit framework and Apple Security framework APIs for Apple Platforms in v2026.05. Adds support for JDK 25 enhancements and Java source code scanning for JSP files in v2026.05. Adds support for Xcode 26.4 on Apple platforms in v2026.04. Adds support for JDK 26 in v2026.04. Adds support for scanning and viewing Java source code on the Veracode platform in v2026.04. Adds support for excluding Java .jar files from static analysis via veracode.json in v2026.04. Expands hardcoded secrets detection to include application configuration files with -local and -prod naming patterns in v2026.04. Adds support for React 19 in v2026.04. Adds support for Kotlin 2.3 in v2026.04. Adds support for Psycopg 3 in Python applications in v2026.04. Adds support for Fast HTTP in Go in v2026.03. Adds support for Angular 20 in v2026.03. Adds support for Next.js 15.x in v2026.03. Adds taint sinks for Flask send_from_directory and send_file functions in Python in v2026.03. Expands .NET taint sink coverage for CWE-80 to include System.Web.UI.Page.Title and System.Web.UI.HtmlControls.HtmlHead.Title in v2026.02. Adds support for Go 1.26 in v2026.02. Adds support for PyYAML in Python in v2026.02. Adds support for excluding specific Java classes from Static Analysis via veracode.json in v2026.02. Adds support for Apex 64 and Apex 65 in v2026.01. Adds support for Spring Boot 4, Spring Core 7, and Spring Security 7 for Java in v2026.01. Adds support for the Svelte framework in JavaScript in v2026.01. Adds support for Ruby 4.0 and Rails 8.1 in v2026.01. Pipeline Scan results.json output now includes finding exploit level as a numeric value from -2 (Very Unlikely) to 2 (Very Likely).
28 details in Everything
Enhanced Python scanner with improved taint tracking, cross-file analysis, and support for PySpark, Flask, Django, FastAPI.
Adds enhanced taint tracking for deeper vulnerability detection in Python applications. Enables cross-file analysis to identify vulnerabilities spanning multiple modules. Adds support for applications built with PySpark, Flask, Django, and FastAPI frameworks.
3 details in Everything
Static Analysis updates (2026-07-21)
Jul 21, 2026
·
issue 022
Veracode Static Analysis July 2026 engine adds Android 17, .NET 10 enhancements, Python httplib SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination.
Adds support for Android 17 in the static analysis engine. Enhances support for .NET 10, including improved analysis of applications using Saturn.dll. Adds support for Python httplib to detect CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. Expands pnpm module support to improve JavaScript dependency resolution. Improves detection of CWE-80 flaws in React Native (JavaScript) applications.
+3 more
show less
Expands third-party library detection for Java to include Fluxnova. Improves JSP and JSF Expression Language modeling using more complete POJO data, potentially surfacing additional valid findings. Improves scan accuracy for code generated by Project Lombok (Java).
8 details in Everything
Veracode Static Analysis Engine v2026.07 adds Android 17 support and expands .NET, Java, and JS detection coverage.
Adds support for Android 17 scanning Enhances analysis of applications that include Saturn.dll Expands third-party library detection to include Fluxnova
3 details in Everything
Veracode CLI v2.51.1 improves packaging support for JavaScript, .NET, Java (Gradle), and Go
Veracode CLI v2.51.1 improves packaging for JavaScript, .NET, and Java Gradle.
Improved packaging support for JavaScript Improved packaging support for .NET Improved packaging support for Java (Gradle) Removed unnecessary warnings in Go packaging
4 details in Everything
Platform updates (2026-07-15)
Jul 15, 2026
·
issue 018
Veracode adds OAuth for XML APIs XML APIs Interfaces for reading, writing, or querying XML documents, provided by libraries such as libxml2 or built into language runtimes; cyber tools use them to parse structured data like configs, reports, or protocol messages reliably. OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
Supports OAuth Client Credentials authentication for Veracode XML APIs, not just REST APIs REST APIs A convention for building HTTP-based interfaces where resources are addressed by URL and manipulated with standard verbs like GET, POST, and DELETE, giving cyber tools a predictable way to integrate with external services. Adds six new built-in security policies to the Veracode Platform, ahead of planned deprecation of recommended and transitional policies. Auto-Update OWASP and Auto-Update CWE Top 25 policy rules now enforce OWASP Top 10:2025 OWASP Top 10:2025 A ranked list of the ten most critical web application risk categories, maintained by the Open Worldwide Application Security Project, used by cyber tools to prioritize detection, testing, and remediation coverage. MITRE MITRE A US federally funded research and development center that maintains public frameworks—ATT&CK, CVE, D3FEND—that cyber tools use to classify threats, vulnerabilities, and defensive techniques in a common language. Adds collections_list field to Finding Reporting API responses, returning collection names associated with an application. Adds Collections fields to the Applications explore in Veracode Analytics, with new Policy Compliance Overview dashboard visualizations.
+18 more
show less
New most_recent_scan filter for the Reporting API Scans report returns only the most recent scan per asset when set to true. New Firewall Usage Dashboard and Explore in Veracode Analytics surface metrics for Veracode Firewall. Policy Settings page adds light and dark mode support. New library_instance_ref field in Reporting API findings response uniquely identifies the specific library instance associated with a finding. New custom_severity filter available for the Reporting API Findings report. New data_refresh_date field added to the Reporting API to indicate the most recent Analytics data refresh time. Supports OAuth 2.0 OAuth 2.0 An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms. Veracode Analytics data refresh interval reduced from four hours to two hours. MPT Flaw Matching correlates Manual Penetration Testing findings across tests for consistent flaw IDs, status values, and remediation grace period inclusion. Administrators can now disable Veracode-defined roles for users who use custom roles, with corresponding Identity API updates. Container and IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. New action_type filter in the Reporting REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. New Audit Log report available in the Reporting REST API for querying user activity from Veracode Analytics. Multiple domains can now be mapped to a single identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. SP-initiated SP-initiated A SAML or OAuth/OIDC login flow where the Service Provider redirects the user to an Identity Provider to authenticate, rather than the IdP pushing an assertion unprompted; tools use it to trigger SSO from their own login page. SAML SSO SAML SSO An authentication protocol that lets a user log in once with an identity provider and access multiple services without re-entering credentials, by passing signed XML assertions between parties. Customizable PDF report now displays SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. Customer Managed Encryption Keys (CMEK) allows encryption of Veracode Platform data using your own root encryption key managed in your KMS KMS A managed service that creates, stores, rotates and controls access to encryption keys, usually backed by HSMs. Applications ask it to encrypt or decrypt rather than holding keys themselves. Administrators can now customize columns in the All Users table on the Administration page. Upgraded Veracode Analytics to Looker 26.6, adding finer widget size granularity, persistent filtering, and tabbed dashboards.
23 details in Everything
└──▷ BREAKING ON UPGRADE
! The /healthcheck/status endpoint has been removed and now returns a 404 error; use the v2/principal endpoint in the Identity REST API to check authenticated connectivity instead.! Success events have been removed from the Firewall dataset in Firewall Analytics.
Platform updates (2026-07-13)
Jul 13, 2026
·
issue 015
Veracode adds OAuth 2.0 OAuth 2.0 An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms.
└──▷ HOW TO FIND IT
Create and manage OAuth 2 OAuth 2 An open authorization framework (RFC 6749) that lets a service grant limited access to a user's resources on another service without exposing credentials, giving cyber tools a standard way to authenticate against third-party APIs.
📍 In the Veracode Platform, go to your account menu › API Credentials, then select Create OAuth 2.0 Client Credentials and copy the generated client ID and secret for use in your integration.
Adds custom_severity filter to the Reporting API Findings report for targeted severity-based querying. Adds six new built-in security policies to the Veracode Platform. Policy Settings page now supports light and dark mode. Reporting REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
4 details in Everything
└──▷ BREAKING ON UPGRADE
! The /healthcheck/status endpoint has been removed and now returns a 404 error; use the v2/principal endpoint in the Identity REST API instead.! Success events have been removed from the Firewall dataset in Veracode Analytics.
Training updates (2026-07-08)
Jul 8, 2026
·
issue 014
Veracode Security Labs adds OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. LLM LLM A large language model, a neural network trained on large amounts of text to recognize patterns and generate language. Applications use it for tasks such as answering, summarizing and writing code.
New Security Labs lesson: OWASP LLM 07: Under the Hood (Flask), expanding the OWASP Top 10 for LLM Applications hands-on lab series. Adds multilingual caption support (English, Spanish, French, Portuguese, Chinese) to the C/C++ Memory Management Risks and Best Practices eLearning course.
2 details in Everything
Package Firewall updates (2026-07-07)
Jul 7, 2026
·
issue 027
Veracode Package Firewall launches with automatic blocking of untrusted packages, now available in the European region.
New Package Firewall service automatically blocks untrusted packages that don't comply with policies across artifact repositories and package managers. Package Firewall mitigates risks from malware, typosquatting typosquatting Using a name close to a trusted domain or software package to catch spelling mistakes. Attackers use it to lure people or installers to a malicious lookalike. Package Firewall is now available in the European region.
3 details in Everything
Integration updates (2026-07-07)
Jul 7, 2026
·
issue 014
GitHub Workflow Integration v2.0.0 adds platform-based install, scan scheduling, and Apex/VB6/Perl autopackaging support.
└──▷ USE IT
Enable debug logging in a GitHub or Azure DevOps workflow to troubleshoot scan failures.
yaml
copy
# In veracode.yml
debug: true
Target a specific analysis branch for scheduled scans in Azure DevOps instead of the default branch.
yaml
copy
# In veracode.yml
analysis_branch: main-security-baseline
Install and configure the GitHub Workflow Integration directly from the Veracode Platform to skip manual GitHub Marketplace steps.
📍 In the Veracode Platform, go to Integrations › GitHub › Install, select your GitHub organization, and complete the configuration to install or update credentials without visiting GitHub Marketplace.
Enables installing and configuring the Veracode GitHub Integration directly from the Veracode Platform, eliminating manual GitHub Marketplace steps. Supports updating integration credentials and adding organizations from the Veracode Platform, regardless of original install method. Adds autopackaging support for Apex, VB6, and Perl in the GitHub Workflow Integration. Enables scheduling Static Analysis, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Adds a Scan Scope setting in Veracode Scan for Visual Studio v0.8.0 to scan the full project directory or only the active solution.
+13 more
show less
Adds usage analytics to Veracode Scan for Visual Studio v0.8.0 and Veracode Scan for JetBrains v1.29.0 for insights into plugin adoption, feature usage, and scan activity. Adds page size support to the Platform Applications API (/appsec/v1/applications) in Java API Wrapper v26.3.19.0 for efficient retrieval of large application lists. Introduces support for the Veracode Platform paginated Sandbox REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Adds the debug configuration option in veracode.yml for the Azure DevOps, GitHub, and GitLab Workflow Integrations for debugging and troubleshooting. Adds support for the Veracode Platform Findings REST API in Java API Wrapper v26.2.18.0 to access open and mitigated application findings. Adds a configurable retry mechanism for the Platform Applications API in Java API Wrapper v26.2.18.0 to handle transient failures and timeouts. Adds support for Visual Studio 2026 in Veracode Scan for Visual Studio v0.7.2. Replaces the deprecated Veracode Flaw Importer task (with spaces) with the new VeracodeFlawImporter task in the Azure DevOps extension v3.35.0. Enables scheduling scans for every organization where the Azure DevOps Workflow Integration is installed, based on veracode.yml configurations (v2.3.9). Ensures that when analysis_branch is specified in veracode.yml, scheduled scans run against that branch instead of the default branch (Azure DevOps Workflow Integration v2.3.10). Ensures SCA scans fail on vulnerability findings when custom policies with Build Action: error are applied in the Veracode Platform (Azure DevOps Workflow Integration v2.3.3). Ensures mitigated findings are excluded from pipeline scan results in Azure DevOps Workflow Integration v2.3.0. Adds Windows-based runner support for the GitHub Workflow Integration.
18 details in Everything
Veracode Azure DevOps extension v3.35.0 introduces VeracodeFlawImporter task to replace deprecated Flaw Importer.
Updates Veracode Azure DevOps extension v3.35.0 for compatibility with future Microsoft TFX packaging library upgrade
1 detail in Everything
Veracode Azure DevOps extension v3.35.0
Jul 7, 2026
· release notes
VeracodeFlawImporter task replaces deprecated Veracode Flaw Importer task
Updates extension compatibility with future Microsoft TFX packaging library.
1 detail in Everything
└──▷ BREAKING ON UPGRADE
! The Veracode Flaw Importer task (with spaces) is deprecated and scheduled for removal in a future release.
Platform updates (2026-07-06)
Jul 6, 2026
·
issue 014
Veracode adds six new built-in policies, OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against. CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. OAuth 2.0 OAuth 2.0 An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms.
└──▷ TRY IT
Verify authenticated connectivity to Veracode after migrating away from the removed /healthcheck/status endpoint.
copy
$ curl -s 'https://api.veracode.com/api/authn/v2/principal' \
  -H 'Authorization: Bearer <token>'
Updates Auto-Update OWASP and Auto-Update CWE Top 25 policy rules to enforce OWASP Top 10:2025 OWASP Top 10:2025 A ranked list of the ten most critical web application risk categories, maintained by the Open Worldwide Application Security Project, used by cyber tools to prioritize detection, testing, and remediation coverage. MITRE MITRE A US federally funded research and development center that maintains public frameworks—ATT&CK, CVE, D3FEND—that cyber tools use to classify threats, vulnerabilities, and defensive techniques in a common language. Adds six new built-in security policies to the platform, ahead of deprecation of recommended and transitional policies. Adds collections_list field to Finding Reporting API responses, returning collection names associated with each application. Adds Collections fields to the Applications explore in Veracode Analytics, with new Collections visualizations in the Policy Compliance Overview dashboard. New most_recent_scan filter for the Reporting API Scans report — when set to true, returns only the most recent scan per asset.
+17 more
show less
Enables creation and management of OAuth 2 OAuth 2 An open authorization framework (RFC 6749) that lets a service grant limited access to a user's resources on another service without exposing credentials, giving cyber tools a standard way to authenticate against third-party APIs. New Firewall Usage Dashboard and Explore in Veracode Analytics surfaces metrics for Veracode Firewall. Adds library_instance_ref field to Reporting API findings responses to uniquely identify the specific library instance tied to a finding. New custom_severity filter available for the Reporting API Findings report. Adds data_refresh_date field to the Reporting API to indicate the most recent Analytics data refresh time. Containers & IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. New action_type filter in the Reporting API Audit Log report for narrowing results by specific user actions. New Audit Log report in the Reporting REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. Supports mapping multiple domains to a single identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. IdP IdP A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. SP-initiated SP-initiated A SAML or OAuth/OIDC login flow where the Service Provider redirects the user to an Identity Provider to authenticate, rather than the IdP pushing an assertion unprompted; tools use it to trigger SSO from their own login page. SAML SSO SAML SSO An authentication protocol that lets a user log in once with an identity provider and access multiple services without re-entering credentials, by passing signed XML assertions between parties. Customizable PDF reports now display SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. Introduces Customer Managed Encryption Keys (CMEK), allowing encryption of Veracode Platform data with your own root key managed in your KMS KMS A managed service that creates, stores, rotates and controls access to encryption keys, usually backed by HSMs. Applications ask it to encrypt or decrypt rather than holding keys themselves. Administrators can now customize columns in the All Users table on the Administration page. Enables disabling Veracode-defined roles for users who use custom roles, providing finer-grained access control. Removes the /healthcheck/status endpoint (now returns 404); practitioners must migrate to the v2/principal Identity REST API endpoint to verify authenticated connectivity. Veracode Analytics data refresh interval reduced from four hours to two hours. Manual Penetration Testing (MPT) Flaw Matching correlates findings across tests for consistent flaw IDs, status values, and grace period support in security policies. Upgrades Veracode Analytics to Looker 26.6, adding finer widget size granularity, persistent filtering, and tabbed dashboards.
22 details in Everything
Veracode CLI v2.51.0 adds --exclude flag to veracode package, target UUID UUID A universally unique identifier, usually a 128-bit value used to identify an object across systems. It is designed to make independently generated identifiers unlikely to collide. IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup.
Adds the --exclude flag to the veracode package command to prevent specified Java packages or JAR files from being scanned The veracode dynamic scan command now supports target UUIDs UUIDs A universally unique identifier, usually a 128-bit value used to identify an object across systems. It is designed to make independently generated identifiers unlikely to collide. Introduces schema enhancements for container and IaC scan results returned by the veracode scan command
3 details in Everything
Veracode adds platform-native GitHub integration install/update and scan scheduling for organizations.
└──▷ HOW TO FIND IT
Install the GitHub integration for a new organization without visiting the marketplace.
📍 Steps: In the Veracode Platform, navigate to Integrations › GitHub Integration › Install.
Update credentials for all organizations at once from the platform UI.
📍 Steps: In the Veracode Platform, go to Integrations › GitHub Integration and update the credentials section.
Schedule a Static Analysis scan for an organization via the platform UI.
📍 Steps: In the Veracode Platform, go to Integrations › GitHub Integration › Schedule and select Static Analysis .
Install and configure the Veracode GitHub Integration directly from the Veracode PlatformUpdate integration credentials from the Veracode Platform Configure scan schedules for Static Analysis, SCA, and IaC from the Veracode PlatformAdded autopackaging support for Apex, VB6, and Perl
4 details in Everything
GitHub Workflow Integration v2.0.0
Jun 30, 2026
· release notes
Veracode GitHub Integration v2.0.0 adds centralized install/config/credentials from Platform and scan scheduling, plus new Apex/VB6/Perl autopackaging.
Adds installation and configuration of the Veracode GitHub Integration directly from the Veracode Platform Adds ability to update integration credentials for all organizations from the Veracode Platform Adds scheduling capability for Static Analysis, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. Adds autopackaging support for Apex, VB6, and Perl
4 details in Everything
Adds six new built-in security policies to the Veracode Platform.
DAST updates (2026-06-26)
Jun 26, 2026
·
issue 014
Veracode DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
└──▷ HOW TO FIND IT
If your scheduling integration uses the old DAST REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
📍 Refer to the DAST API specification for the updated scheduling endpoint paths, then update any REST calls that previously targeted the old schedule management endpoints (e.g., replace deprecated schedule routes with the new ones documented in the DAST API spec).
Adds Directory Restrictions to DAST target configuration, giving practitioners control over scan scope by limiting which directories are crawled. Introduces enhanced DAST Schedule configuration with advanced scheduling options and greater flexibility; all existing schedules are automatically migrated. Breaking change: DAST REST API scheduling endpoints have changed — integrations managing schedules via the REST API must be updated to the new endpoints. Enables open-port scanning for web applications in Dynamic Analysis and DAST Enterprise mode. Adds new scan engine detections for HTTP headers, TLS, and fingerprinting in Dynamic Analysis and DAST Enterprise mode.
5 details in Everything
Static Analysis updates (2026-06-24)
Jun 24, 2026
·
issue 014
Veracode SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment. CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
Adds support for Dart 3.12 and Flutter 3.44 in static analysis. Adds support for Kotlin 2.4. Improves classification of first-party .NET assemblies to better distinguish application code from third-party dependencies. Improves detection of vulnerabilities involving tainted data flows through public Apex methods. Improves support for Apple Security framework APIs.
+4 more
show less
Improves detection of CWE-532 flaws in Apex. Improves detection of CWE-918 (SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly. Improves detection of CWE-73 flaws in JavaScript. Improves detection of CWE-259 and CWE-798 (hardcoded credential) flaws across all languages to reduce false positives.
9 details in Everything
Veracode adds DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces. REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Enhances DAST Schedule with advanced scheduling capabilities, including automatic migration of existing schedules
1 detail in Everything
└──▷ BREAKING ON UPGRADE
! DAST REST API scheduling endpoints have changed; integrations using these endpoints must update to the new URLs.
New DAST Directory Restrictions and Schedule enhancements
Jun 24, 2026
· release notes
New DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Adds Directory Restrictions in target configuration to control the scan scope Enhances the DAST Schedule feature with advanced scheduling capabilities and configuration options
2 details in Everything
Adds Dart 3.12/Flutter 3.44 and Kotlin 2.4 support; improves third-party detection across multiple languages
Improves detection of vulnerabilities that involve tainted data flows through public methods in Apex. Improves detection of CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. Improves support for Security APIs on Apple Platforms. Improves third-party detection in Java, JavaScript, and Python. Improves detection and classification of ForgeRock third-party dependencies in Maven-based projects in Java.
+5 more
show less
Improves detection of CWE-918 flaws in Java. Improves detection of CWE-73 flaws in JavaScript. Improves classification of first-party .NET assemblies to distinguish application code from third-party dependencies. Improves detection of CWE-259 and CWE-798 flaws across all languages to reduce false positives. Improves RPG parsing.
10 details in Everything
Veracode Scan for Visual Studio v0.8.0 adds Scan Scope setting and usage analytics
└──▷ HOW TO FIND IT
Limit a Veracode scan to only the currently open solution in Visual Studio for faster feedback.
📍 In the Veracode Scan extension settings pane, open Scan Scope and select Active Solution .
Adds a Scan Scope setting in the extension UI to limit scans to the active solution instead of the full project directory Adds usage analytics reporting plugin adoption, feature usage, and scan activity
2 details in Everything
Veracode Scan for Visual Studio v0.8.0
May 27, 2026
· release notes
Version 0.8.0 introduces UI configuration for scan scope and background telemetry analytics.
Looker 26.6 upgrade brings finer granularity in widget sizes and persistent filtering to Veracode Analytics dashboards.
Adds support for finer granularity in widget sizes within Looker dashboards Enables persistent filtering on dashboard widgets Introduces tabbed dashboards for organizing multiple views
3 details in Everything
Static Analysis Engine v2026.05 adds CloudKit and Apple Security framework support for Apple Platforms.
Adds CloudKit framework support for Apple Platform scanning Adds Apple Security framework APIs support for Apple Platform scanning
2 details in Everything
VRM May 2026 adds automated workflows (patterns), MPT issue details, Apps CSV export, and Assets IP view.
Adds Patterns to VRM settings for automated workflows: assign assets to applications, assign labels to assets, create tickets from issues, or update issue status Adds Details fields (Severity, Exploit, Remediation, Location) to Manual Penetration Testing (MPT) issues in the VRM UI Allows exporting the Applications table with custom filters as a CSV file via the VRM console Enables searching by Target Name in the Solutions table in the VRM console
4 details in Everything
New collections_list field to the Finding Reporting API
May 26, 2026
· release notes
Veracode Finding Reporting API adds collections_list field to responses
New most_recent_scan filter available for the Reporting API Scans report
May 18, 2026
· release notes
New most_recent_scan filter for Veracode Reporting API Scans report
Limits scan results to only the latest entry per asset when most_recent_scan=true, eliminating client-side filtering.
1 detail in Everything
Support for OAuth 2.0 Client credentials on the API Credentials page
Apr 30, 2026
· release notes
Adds OAuth 2.0 OAuth 2.0 An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms.
Veracome Static Analysis Engine v2026.04 adds support for JDK 26, React 19, Kotlin 2.3, Java source scanning, and .jar exclusion via veracode.json.
Adds veracode.json config key to exclude .jar files from static analysis Adds support for viewing Java source code on the platform Adds support for JDK 26, React 19, Kotlin 2.3, Xcode 26.4, Dart 3.11, Flutter 3.41, and Psycopg 3 Expands hardcoded secrets detection to include application configuration files with -local and -prod naming patterns
4 details in Everything
Security Labs – updates to the Get Lesson Progress API
Apr 21, 2026
· release notes
Get Lesson Progress API adds stack, updatedOn, and filter parameters for incremental loads
Adds stack field to the Get Lesson Progress API response payload. Adds updated_on field to the Get Lesson Progress API response payload. Adds updatedAfter query parameter to the Get Lesson Progress API to support incremental loads. Adds excludeNotStarted=true query parameter to the Get Lesson Progress API to remove unstarted lessons from results.
4 details in Everything
Veracode CLI v2.49.0 adds new exit codes for CI/CD automation and improved SQL packaging detection.
Adds exit codes 5, 6, and 7 to the veracode package command to signal packaging or build issues in CI/CD pipelines Enhances Static Packager with better detection of supported and unsupported SQL dialects during packaging
2 details in Everything
Veracode CLI v2.48.0 adds --skip-packagers flag and exit codes to package discover, improving GitLab repo scan performance
└──▷ USE IT
Package results while excluding unsupported SQL artifacts to keep the bundle clean.
shell
copy
veracode package --skip-packagers
Automate checks on whether package discover succeeded or failed in a CI pipeline using its exit code.
shell
copy
veracode package discover; echo $?
veracode package introduces --skip-packagers flag to exclude specific artifacts like unsupported SQL from packagingveracode package adds support for requirements-dev.txt in Python packaging workflows to include development dependenciesveracode package discover introduces exit codes to report status programmatically
3 details in Everything
Azure DevOps Workflow Integration v2.3.9
Apr 13, 2026
· release notes
Azure DevOps Workflow Integration v2.3.9 adds per-organization scan scheduling via veracode.yml.
veracode.yml now supports schedule configuration to trigger scans for every organization where the integration is installed.Users can define scan schedules in veracode.yml without using the web UI, enabling automated CI/CD pipeline integration.
2 details in Everything
Veracode CLI v2.48.0 adds --skip-packagers to package, requirements-dev.txt support, and exit codes to package discover
Adds the --skip-packagers flag to veracode package to exclude specific artifacts like unsupported SQL from packaging without affecting other languages Adds support for requirements-dev.txt in Python packaging workflows to include development dependencies
2 details in Everything
Adds --show-cli flag to SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
New SCA agent scan option to link results to an application profile
Mar 31, 2026
· release notes
New --appname flag in SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it.
Adds --appname flag to the SCA agent scan command to link results to an application profile Requires authentication with Veracode using OAuth or HMAC for the new app name linking feature
2 details in Everything
New VRM table capabilities: CSV export with filters, IP address column, and Target Name search
Export the Applications table with custom filters applied as a CSV file. View IP addresses in the Assets table in a dedicated column. Search by Target Name in the Solutions table.
3 details in Everything
Assign policies to SCA Agent-based Scan workspaces
Mar 23, 2026
· release notes
Assign Unified Policies to SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Security Labs users and teams is integrated with the Veracode Platform
Mar 23, 2026
· release notes
Security Labs users and teams integrated with Veracode Platform via IAM IAM Identity and Access Management — a framework of policies and services for controlling who can authenticate to systems and what resources they are authorized to use, letting cyber tools enforce least-privilege and audit access.
Adds authentication of Security Labs users through Veracode IAM, allowing administrators to manage user access from the Veracode Platform. Enables access to Security Labs under the Security Training section of the Veracode Platform for migrated customers.
2 details in Everything
Veracode adds pagination to Applications and Sandboxes APIs via page size support.
Adds page_size parameter to the Platform Applications API (/appsec/v1/applications) for efficient large list retrieval
1 detail in Everything
Veracode CLI v2.47.0 adds Poetry support for autopackaging and improved false positive reduction
Adds Poetry package management tool support to the veracode package command for Python autopackaging Improves veracode scan precision by reducing false positives
2 details in Everything
Veracode CLI v2.47.0 adds Poetry support to veracode package and improves false positive reduction.
veracode scan returns more precise findings by reducing false positives
1 detail in Everything
Veracode Scan for Visual Studio v0.7.2
Mar 12, 2026
· release notes
Veracode Scan for Visual Studio v0.7.2 adds VS 2026 support and single best-fix recommendations.
Secure coding language addendum courses
Mar 4, 2026
· release notes
Veracode adds OWASP Top 10:2025 OWASP Top 10:2025 A ranked list of the ten most critical web application risk categories, maintained by the Open Worldwide Application Security Project, used by cyber tools to prioritize detection, testing, and remediation coverage.
New field added to the Veracode Reporting API findings response
Mar 2, 2026
· release notes
Veracode Reporting API findings response adds library_instance_ref field
Static Analysis Engine v2026.02 adds veracode.json exclusion config, Go 1.26 and .NET taint coverage.
Adds veracode.json configuration file support to exclude specific Java classes from Static Analysis Adds taint propagation support for framework APIs for Apple Platforms Adds support for Go 1.26 in the Static Analysis Engine Expands .NET taint sink coverage for CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. System.Web.UI.Page.Title and System.Web.UI.HtmlControls.HtmlHead.Title
4 details in Everything
Veracode CLI v2.46.0 adds --java-source for Java packaging and Gradle detection in discover
└──▷ USE IT
Force Java source packaging via environment variable when running the package command.
shell
copy
VERACODE_PACKAGE_JAVA_SOURCE=true veracode package --project "MyApp" --profile "default"
Adds --java-source flag to veracode package command (and VERACODE_PACKAGE_JAVA_SOURCE=true env var) to explicitly package Java source code. Adds gradle support in the toolchain detection logic of veracode package discover for Java projects using the Gradle package manager.
2 details in Everything
Veracode CLI v2.46.0 adds Java source packaging and Gradle discovery
DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
└──▷ BREAKING ON UPGRADE
! The legacy Full scan option is deprecated and no longer available when creating new DAST targets or configuring Quick scan targets.
DAST target creation now uses Enterprise mode by default
Feb 12, 2026
· release notes
DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
DAST target creation now uses Full scan Enterprise mode by defaultLegacy Full scan option deprecated and no longer available for new targets or Quick scan configurations
2 details in Everything
└──▷ BREAKING ON UPGRADE
! The legacy Full scan option is no longer available when creating new targets or configuring Quick scan targets
Veracode Java API Wrapper adds configurable retry logic for Apps API and support for Findings REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Implements a configurable retry mechanism for the appsec/v1/applications endpoint to improve handling of transient failures, timeouts, and intermittent network issues. Adds support for the Veracode Platform Findings REST API to access open and mitigated application findings.
2 details in Everything
Veracode Java API Wrapper v26.2.18.0 adds Findings REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Adds support for the Veracode Platform Findings REST API to access open and mitigated application findings Implements a configurable retry mechanism for the Veracode Platform Applications API (appsec/v1/applications) to improve handling of transient failures, timeouts, and intermittent network issues
2 details in Everything
New Findings view, enhanced prioritization workflows, and expanded reporting capabilities added to the Veracode service.
Added a new Findings view for security data management Enhanced prioritization workflows to help prioritize remediation Expanded reporting capabilities for actionable insights
3 details in Everything
Veracode CLI v2.45.0 adds disk token reading, prioritizes NVD NVD The National Vulnerability Database, maintained by NIST, is the U.S. government repository of CVE records enriched with CVSS scores and metadata; cyber tools query it to drive vulnerability prioritization.
veracode scan now prioritizes vulnerability results from the NVD database when available.veracode scan now categorizes secret-type findings as Critical in scan results.All Veracode CLI commands can consistently read access tokens access tokens A credential that authorizes a client to use a service or API. It usually has limited permissions and a lifetime; anyone holding it may be able to use those permissions.
3 details in Everything
Veracode GitLab Workflow Integration v2.1.4 adds debug config option in veracode.yml
GitLab Workflow Integration v2.1.4
Jan 29, 2026
· release notes
Adds debug config option in veracode.yml for troubleshooting
Veracome Static Analysis Engine v2026.01 adds Apex 64/65, Spring Boot 4, Svelte, and Ruby on Rails 8.1 support.
Adds Apex 64 and Apex 65 platform support to the Static Analysis Engine for Salesforce code scanning. Adds support for Spring Boot 4 , Spring Core 7 , and Spring Security 7 in Java scan coverage. Adds detection capabilities for the Svelte framework in JavaScript scans. Adds support for Ruby 4.0 and Rails 8.1 in Ruby on Rails code scanning.
4 details in Everything
Veracode Scan Engine adds open port scanning, HTTP header/TLS/fingerprinting detections in Dynamic Analysis DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
└──▷ HOW TO FIND IT
Enable open port scanning in Dynamic Analysis to identify exposed services during DAST Enterprise scans.
📍 In the scan configuration for Dynamic Analysis (DAST Enterprise Mode), enable the 'scan for open ports' option.
Review newly detected HTTP header, TLS, and fingerprinting issues in your DAST Enterprise scan reports.
📍 Run a new Dynamic Analysis (DAST Enterprise Mode) scan on your web application and check the results for HTTP headers , TLS , and fingerprinting findings.
Dynamic Analysis and DAST Enterprise Mode now support scanning web applications for open ports. Scan engine includes new detections for HTTP headers, TLS, and fingerprinting.
2 details in Everything
Veracode adds open port scanning, HTTP header, TLS, and fingerprinting detections to Dynamic Analysis DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Dynamic Analysis and DAST Enterprise Mode now support scanning web applications for open ports New detections for HTTP headers, TLS, and fingerprinting in the scan engine
2 details in Everything
New custom_severity filter available for the Reporting API Findings report
Jan 20, 2026
· release notes
New custom_severity filter available for the Reporting API Findings report
Azure DevOps Workflow Integration v2.3.3
Jan 16, 2026
· release notes
SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. error Build Action is configured.
Build Action: error configuration for SCA agent-based scans now fails the scan when vulnerabilities are foundCustom policies applied in Veracode Platform trigger failure behavior for SCA agent scans
2 details in Everything
Veracode CLI v2.44.0 adds veracode package discover, custom policy enforcement to scan, and SRCLR_MAKE_WINDOWS env var
Introduces the veracode package discover command to detect toolchains for scannable artifacts. Adds SRCLR_MAKE_WINDOWS environment variable to enable preprocessing C/C++ source files with Make on Windows using native gcc or clang.
2 details in Everything
Updates to Reporting API metadata and Swagger documentation
Dec 19, 2025
· release notes
Veracode adds data_refresh_date field to Reporting API and updates Swagger docs for UTC filtering.
Adds data_refresh_date field to the Reporting API response to indicate when Analytics data was last refreshed Updates Reporting API Swagger documentation to reflect that datetime filtering uses UTC
2 details in Everything
Support added for OAuth 2.0 client credentials flow
Dec 18, 2025
· release notes
Adds OAuth 2.0 OAuth 2.0 An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms.
Static Analysis Engine v2025.12 adds .NET 10, Go Fiber, Dart 3.10/Flutter 3.38 and Swift standard library taint propagation.
Adds support for .NET 10 Adds support for the Go Fiber web framework Adds support for Dart 3.10 and Flutter 3.38
3 details in Everything
Veracode Scan for Visual Studio v0.7.0 adds IDE integration for importing static scan results and proposing mitigations
Imports static scan results from the Veracode Platform directly into the IDE Proposes mitigations for static scan flaws directly within the IDE
2 details in Everything
Veracode Scan for Visual Studio v0.7.0
Dec 11, 2025
· release notes
Veracode Scan for Visual Studio v0.7.0 enables importing static scan results and proposing mitigations in-IDE.
Imports static scan results from the Veracode Platform directly into the IDE Proposes mitigations for static scan flaws directly within the IDE
2 details in Everything
Veracode Static Analysis v2025.11 adds AWS Glue support and enhances detection accuracy across languages.
Enhances identification of first-party code in WEB-INF/classes with non-standard or mismatched package names (Java)
1 detail in Everything
Veracode Scan for JetBrains v1.6.0 introduces importing static scan results and proposing mitigations directly in the IDE.
Veracode Scan for JetBrains v1.6.0 allows importing static scan results from the Veracode Platform directly into the IDE Veracode Scan for JetBrains v1.6.0 proposes mitigations for static scan flaws directly within the IDE
2 details in Everything
Veracode Scan for JetBrains v1.6.0
Nov 18, 2025
· release notes
Veracode Scan for JetBrains v1.6.0 adds IDE-native import of static scan results and flaw mitigation proposals.
Adds direct import of static scan results from the Veracode Platform into the JetBrains IDE Adds in-IDE proposal of mitigations for static scan flaws
2 details in Everything
Veracode releases Package Firewall to block untrusted packages across artifact repositories.
Veracode CLI v2.43.0 adds VERACODE_PACKAGE_GOLANG_GENERATE env var for client-side CGO and Apex generic packaging support
└──▷ USE IT
Enable CGO code generation locally for Go applications packaged with the Veracode CLI.
shell
copy
export VERACODE_PACKAGE_GOLANG_GENERATE=true
veracode package
Adds the VERACODE_PACKAGE_GOLANG_GENERATE environment variable to enable client-side CGO code generation when packaging Go applications. The veracode package command now supports a generic packager for Apex.
2 details in Everything
Veracode CLI v2.43.0 adds VERACODE_PACKAGE_GOLANG_GENERATE env var for client-side CGO generation and generic Apex packager support.
Adds VERACODE_PACKAGE_GOLANG_GENERATE environment variable to enable client-side CGO code generation when packaging Go applications Supports generic packager for Apex in the veracode package command
2 details in Everything
New look for Veracode Platform pages
Oct 27, 2025
· release notes
Veracode Platform pages now support light and dark mode themes.
Adds light and dark theme support to the UI for All Applications, Add New Application, and Edit Application pages.
1 detail in Everything
Veracode Azure DevOps extension v3.33.0 adds automatic SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
└──▷ HOW TO FIND IT
Allow the extension to automatically handle lifecycle management for SCA findings without manual intervention.
📍 Upgrade to Azure DevOps extension v3.33.0 and allow the automatic tagging logic to run on subsequent flaw imports.
Enables automatic closure of remediated SCA vulnerability work items in Azure DevOps
1 detail in Everything
Veracode Azure DevOps extension v3.33.0
Oct 23, 2025
· release notes
Adds Node.js 20 support and automatic work item closure for remediated SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds Node.js version 20 support Enables automatic closure of work items for remediated SCA vulnerabilities
2 details in Everything
Important note for upgrading to Azure DevOps extension v3.33.0
Oct 23, 2025
· release notes
Azure DevOps extension v3.33.0 adds automated tagging and auto-closure for SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds automatic tagging of SCA work items in Azure DevOps to enable tracking of active findings Enables automatic closure of SCA work items when their associated findings are remediated
2 details in Everything
Static Analysis Engine v2025.10 adds Semantic Kernel, PySpark, DynamoDB, and FastAPI support with new detection engines.
Adds .NET support for Semantic Kernel KernelContent and Taint Injection Adds .NET improved detection of third-party code Adds .NET improved detection of CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. Adds Android skipping of ProGuard-obfuscated classes Adds Android optimized scan performance to reduce analysis time
+8 more
show less
Adds C/C++ improved detection of CWE-73 flaws Adds COBOL automatic copybook detection via enhanced parsing Adds Java improved detection of CWE-611 flaws Adds Java enhanced identification of third-party code Adds Python support for PySpark Adds Python support for DynamoDB Adds Python support for FastAPI Adds cross-language improved detection of CWE-259 and CWE-798 flaws
13 details in Everything
Secure coding language addendum courses
Oct 15, 2025
· release notes
Veracode adds OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against.
Veracode adds assessment quiz courses for learning paths in English, Portuguese, and Spanish.
Veracode Scan for Visual Studio v0.6.0 adds OAuth/SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management.
Veracode Scan for Visual Studio v0.6.0
Oct 9, 2025
· release notes
Veracode Scan for Visual Studio v0.6.0 adds OAuth/SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management.
Veracode Scan for VS Code gains OAuth SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management.
Adds OAuth-based authentication support to Veracode Scan for VS Code v1.15.0 for IDE single sign-on single sign-on Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. Adds email notification on import failure in Veracode Integration for Jira Server v4.14.0 using Jira SMTP SMTP The application-layer protocol used to send email between servers and from clients to servers; cyber tools use it to relay alerts, phishing simulations, or exfiltrated data over standard mail infrastructure.
2 details in Everything
Static Analysis Engine v2025.09 adds Semantic Kernel support, JDK 25, and diagnostic capture in iOS archives
Adds --capture flag to Gen IR for including diagnostic data in .xcarchive files on iOS. Adds support for Semantic Kernel (SK) InvocationFilter and Filter in .NET scanning. Adds support for JDK 25 (LTS) in Java scanning.
3 details in Everything
└──▷ BREAKING ON UPGRADE
! Removes the ability to select third-party modules for scanning.
Veracode Integration for Jira Server v4.14.0
Sep 25, 2025
· release notes
Adds email notifications for failed imports in Veracode Integration for Jira Server v4.14.0
Adds support for sending email notifications when an import fails, using your Jira SMTP SMTP The application-layer protocol used to send email between servers and from clients to servers; cyber tools use it to relay alerts, phishing simulations, or exfiltrated data over standard mail infrastructure.
1 detail in Everything
Veracode Scan for VS Code v1.15.0 adds OAuth-based authentication and single sign-on single sign-on Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management.
GCP asset and findings updates for September
Sep 23, 2025
· release notes
VRM adds GCP asset and findings sources: Cloud SQL, roles, projects, and Security Command Center.
Adds GCP Cloud SQL database as a supported asset source in VRM Adds GCP roles as a supported asset source in VRM Adds GCP projects as a supported asset source in VRM Adds GCP Security Command Center as a supported findings source in VRM
4 details in Everything
GitHub Workflow Integration v0.2.23 updates pipeline scan logic and status reporting
Mitigated findings no longer block new pipeline scans
1 detail in Everything
Veracode EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do.
Adds Business units capability to create, assign, and manage business units with domain associations. Adds Heatmap, World map, and Things widgets to the EASM dashboard with filterable data views. Adds shortcut to create reports from the new Dashboard widgets. Enhances Deep discovery with a work queue, selection toggles, and clearer result indicators.
4 details in Everything
EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do.
Dashboard now supports Heatmap, World map, and Things widgets with filterable data views and report generation shortcutsUsers can create, assign, and manage Business units linked to specific domains Deep discovery features an enhanced work queue with selection toggles and clearer result indicators
3 details in Everything
Veracode VRM simplifies issue URLs by removing connector ID segments
Issue URLs in VRM are simplified by removing connector ID information; the unique issue identifier is now sufficient for routing.
1 detail in Everything
New learning path Scan and fix in your IDE for Veracode Scan for JetBrains setup
Veracode Scan for Eclipse v1.4.0 adds OAuth/SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management.
Verac Integration for Jira Cloud v4.19.0 replaces deprecated Atlassian search API with JQL search API
Integration for Jira Cloud v4.19.0 now uses the JQL search API, replacing the previously used Atlassian search API
1 detail in Everything
Manual Penetration Testing Flaw Matching
Sep 2, 2025
· release notes
New MPT Flaw Matching correlates manual pentest findings with consistent IDs and status values for policy enforcement.
MPT Flaw Matching is a new feature that correlates findings across tests to provide consistent flaw IDs MPT Flaw Matching is a new feature that correlates findings across tests to provide consistent status values Adds ability to include MPT findings in remediation grace periods for security policies
3 details in Everything
Refreshed UI for the DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Static Analysis Engine v2025.08 adds .NET Semantic Kernel detection, Azure Functions isolated process support, and new language/platform coverage.
static-analysis-engine-v202508 adds .NET Semantic Kernel (SK) flaw detection for hardcoded credentials (CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. static-analysis-engine-v202508 extends platform coverage to include Dart 3.8, Flutter 3.32, Go 1.25, Node.js 22.x, Scala 3.7, and Micronaut 4.x.static-analysis-engine-v202508 introduces enhanced CWE-918 detection with reduced false positives for Java/Quarkus scenarios.
3 details in Everything
Pipeline Scan output now displays the finding exploit level
Aug 4, 2025
· release notes
Pipeline Scan results.json now includes finding exploit level (-2 to 2) for CLI/API users.
Adds finding exploit level field to Pipeline Scan's results.json output file Introduces numeric exploit severity scale from -2 (Very Unlikely) to 2 (Very Likely) in scan results
2 details in Everything
Veracode CLI v2.42.0 adds static engine version display, MSBuild .NET packaging, and relative path scan support
Disable Veracode-defined roles for users with custom roles
Jul 8, 2025
· release notes
Disable Veracode-defined roles for users with custom roles
Veracode CLI v2.41.0 adds auth login for OAuth2 OAuth2 An open authorization framework (RFC 6749) that lets a service grant limited access to a user's resources on another service without exposing credentials, giving cyber tools a standard way to authenticate against third-party APIs. SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Introduces veracode auth login command for seamless user onboarding via OAuth2 Adds CycloneDX 1.6 CycloneDX 1.6 An OWASP-maintained Software Bill of Materials standard that catalogs components, dependencies, and supply-chain metadata; tools use it to produce or consume machine-readable SBOMs in a widely supported schema. SPDX 2.3 SPDX 2.3 An open standard from the Linux Foundation for describing software bills of materials, letting cyber tools exchange dependency, license, and vulnerability data in a common machine-readable format. veracode sca SBOM generation Adds ability to include directory path in artifact name with veracode package
3 details in Everything
Veracode CLI v2.41.0 adds auth login, custom vuln DB paths, and improved package/sca capabilities.
Introduces the auth login command to support seamless onboarding via OAuth2 OAuth2 An open authorization framework (RFC 6749) that lets a service grant limited access to a user's resources on another service without exposing credentials, giving cyber tools a standard way to authenticate against third-party APIs. Adds the ability for the veracode scan command to specify a custom location for vulnerability database downloads Enables SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. CycloneDX 1.6 CycloneDX 1.6 An OWASP-maintained Software Bill of Materials standard that catalogs components, dependencies, and supply-chain metadata; tools use it to produce or consume machine-readable SBOMs in a widely supported schema. SPDX 2.3 SPDX 2.3 An open standard from the Linux Foundation for describing software bills of materials, letting cyber tools exchange dependency, license, and vulnerability data in a common machine-readable format. veracode sca command
3 details in Everything
Export web applications from EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do. DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Adds the ability to export web application assets from EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do. DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Adds the capability to mark discovered EASM assets as DAST Candidates to create scan targets in DAST Essentials Adds an export workflow allowing web applications identified in EASM to be transferred directly into the DAST Essentials engine
2 details in Everything
Veracode Fix gains COBOL support with suggested fixes and CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
└──▷ HOW TO FIND IT
View suggested fixes for COBOL vulnerabilities directly in Visual Studio Code during development.
📍 In VS Code, open a COBOL file with detected issues; click the lightbulb icon to see suggested fixes provided by Veracode Fix.
Adds suggested_fixes for COBOL in Veracode Fix Detects CWE-78, 209, 248, 489, and 252 in COBOL code Enables COBOL support in the Veracode CLI Enables COBOL support in IDEs (VS Code, Visual Studio, JetBrains)
4 details in Everything
Support for COBOL and additional CWEs
Jun 27, 2025
· release notes
Veracode Fix adds COBOL support with new detections and CLI/IDE availability
Adds suggested fix generation for COBOL source code in Veracode Fix Adds CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
2 details in Everything
Change to last_updated_date in Reporting REST API Scans object
Jun 25, 2025
· release notes
Reporting REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. last_updated_date now includes post-publish scan name changes
Updates last_updated_date in the Reporting REST API Scans object to include modifications made to scans after they have been published. Ensures last_updated_date reflects updates to scan names.
2 details in Everything
Veracode Scan for VS Code v1.14.1 adds application profile search and scan paging
└──▷ HOW TO FIND IT
Quickly find a specific application profile without navigating away from your current file.
📍 Open the command palette (Ctrl+Shift+P) and type Veracode: Search Application Profiles
Ensure no flaws are truncated by using the paged scan results view.
📍 In the Veracode Scan panel, ensure Show All Flaws is checked to trigger pagination for large scans
Adds direct searching of application profiles within the VS Code IDE via the new search UI Enables pagination in flaw fetching to ensure complete results during scans
2 details in Everything
VS Code extension adds app profile search, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds the ability to search application profiles directly within the VS Code IDE Excludes node_modules files from scan searches by default Adds paging support to ensure all flaws are fetched during scans Displays custom error messages when no supported package manager or build system is detected during SCA agent scans
4 details in Everything
Veracode DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
└──▷ HOW TO FIND IT
Download the latest report for a completed DAST Enterprise scan to review findings offline.
📍 In the console, navigate to Scans › Select your DAST Enterprise scan › Reports tab › click Download
Enhanced reporting capabilities in DAST Enterprise mode
Jun 9, 2025
· release notes
Veracode DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Veracode Scan for VS Code v1.14 adds in-IDE result import and mitigation proposals; Jira integration improves logging/perf.
Adds Import static scan results from the Veracode Platform directly into the IDE to Veracode Scan for VS Code Adds Propose mitigations for static scan flaws directly within the IDE to Veracode Scan for VS Code
2 details in Everything
Veracode Scan for VS Code v1.14.0 adds importing static scan results and proposing mitigations directly in the IDE
Imports static scan results from the Veracode Platform directly into the IDE Proposes mitigations for static scan flaws directly within the IDE
2 details in Everything
Containers & IaC scan results available on Veracode Platform
May 29, 2025
· release notes
Veracode Platform now displays CLI-performed container and IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup.
Displays the results of container and IaC scans, performed from the CLI, on the Veracode Platform Provides the severity count of scan findings, categorized as critical, high, medium, and low Allows you to filter and search findings Presents scan history for each asset to help you track changes in findings reported
4 details in Everything
New action_type filter in the Audit Log report available for the Reporting API
May 27, 2025
· release notes
New action_type filter in Veracode Reporting API Audit Log report
Adds action_type query parameter to the Reporting REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
1 detail in Everything
Updated language and framework support
May 22, 2025
· release notes
Veracode updates support for .NET 9, Android 15, Kotlin 2.1, GCC 14.2.0, and PHP case-sensitive paths.
Adds support for .NET 9 analysis Adds support for Android 15 analysis Adds support for Kotlin 2.1 analysis Adds support for GCC 14.2.0 compiler in C/C++ scanning Adds support for HP TNS Timed Input and Output constructs in COBOL
+2 more
show less
Adds support for HP TNS EXTENDED-STORAGE sections in COBOL Enables case-sensitive file path identification for PHP flaw matching
7 details in Everything
└──▷ BREAKING ON UPGRADE
! PHP files with uppercase letters in their filenames are assigned new flaw IDs due to updated case-sensitive path matching.
Adds Windows Runner support to Azure DevOps Workflow Integration v2.2.1
└──▷ HOW TO FIND IT
Run Veracode analysis jobs on Windows runners within an Azure DevOps pipeline.
📍 Use the Azure DevOps Workflow Integration v2.2.1 task in your pipeline YAML on a Windows agent
New GitLab Workflow Integration enables automated Static, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup.
└──▷ HOW TO FIND IT
Access the new GitLab integration to automate scanning across your repository fleet.
📍 Contact Veracode Technical Support to request access to GitLab Workflow Integration
GitLab Workflow Integration automates scans for thousands of repositories from a single locationGitLab Workflow Integration allows Static Analysis, Software Composition Analysis (SCA), and Infrastructure as Code (IaC) scans in a single workflowGitLab Workflow Integration eliminates the need to configure workflows for individual repositoriesSupports autopackaging for Java, .NET, JavaScript, and Python repositories within the GitLab integration
4 details in Everything
Veracode Scan for Eclipse v1.3.5 adds COBOL and JSP fix suggestions and a new SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds Veracode Fix support for generating flaw suggestions in COBOL projects. Adds Veracode Fix support for generating flaw suggestions for flaws identified in JSP files. Enables skipping the vulnerable method analysis during scans in your IDE. Changes the SCA agent download source from Download.sourceclear.com to Sca-downloads.veracode.com.
4 details in Everything
New Audit log report available for the Reporting API
May 6, 2025
· release notes
Reporting REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Veracode introduces a new EASM EASM External Attack Surface Management: a discipline and category of tooling that continuously discovers and monitors an organization's internet-facing assets to identify exposures before attackers do.
Veracode DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
└──▷ HOW TO FIND IT
Configure AI-assisted authentication for a DAST scan in the Veracode console to simplify setup for complex apps.
📍 In the DAST Enterprise configuration, select AI-Assisted Login under Authentication settings.
Allows DAST scans to handle complex login flows without requiring manually recorded login scripts.
1 detail in Everything
DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
SCA Upload support for Python's Poetry package manager
Apr 25, 2025
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Updated language and framework support
Apr 24, 2025
· release notes
Veracode adds support for JDK 24, Angular 19, Azure Functions v4 and enhances detection performance across multiple platforms.
Added support for JDK 24 Added support for Angular 19 Added support for Azure Functions v4
3 details in Everything
Veracode Scan for JetBrains v1.4.8 adds option to skip vulnerable method analysis
skip.vulnerableMethodAnalysis config key allows skipping vulnerable method analysis during SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
1 detail in Everything
Veracode Scan for JetBrains v1.4.8
Apr 21, 2025
· release notes
Veracode Scan for JetBrains v1.4.8 adds option to skip vulnerable method analysis in SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds the ability to skip vulnerable method analysis during SCA scans. Adds a null check to improve reliability during the module selection process.
2 details in Everything
SCA agent-based scans support for Python's Poetry package manager
Apr 21, 2025
· release notes
SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds detection of malicious packages to Veracode SCA upload scans. Adds detection of malicious packages to Veracode SCA agent-based scans.
2 details in Everything
Veracode CLI v2.39.0 adds --strict flag to veracode package, new C/C++ preparsing, and schema updates for scan results.
Adds the optional --strict flag to the veracode package command, returning exit code 4 on build failures Makes preprocessed source code scanning the default method for C/C++ projects on Windows in the veracode package command Sets the SRCCLR_DOWNLOAD_URL environment variable default to https://sca-downloads.veracode.com, deprecating https://download.sourceclear.com Includes new configuration options for specifying platform and build configuration for C/C++ on Linux and Windows in the veracode package command Implements a new schema for organizing and presenting scan results in the veracode scan command
5 details in Everything
Veracode CLI v2.39.0 adds --strict flag, C/C++ preprocessed scanning defaults, and new scan result schema
veracode package gains --strict flag to return exit code 4 on build failures.C/C++ projects on Windows default to preprocessed source code scanning for broader support and speed. Support for scanning preprocessed C/C++ source code is now available on Linux. SRCCLR_DOWNLOAD_URL environment variable defaults to https://sca-downloads.veracode.com (previous URL deprecated).veracode scan results use a new schema improving organization and presentation.
5 details in Everything
Fix Usage Veracode dashboard now available in European Region
Apr 8, 2025
· release notes
Fix Usage dashboard is now available in the European Region for monitoring developer usage of Veracode Fix.
Adds availability of the Fix Usage analytics dashboard in the European Region.
1 detail in Everything
Azure DevOps Workflow Integration revamp v2.0.0
Apr 3, 2025
· release notes
Azure DevOps Workflow Integration v2.0 allows single-workflow Static, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup.
Enables Static, SCA, and infrastructure as code (IaC) scans in a single workflow Supports autopackaging for Java, .NET, JavaScript, Python, Go, Kotlin, and React Native repositories
2 details in Everything
DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
└──▷ HOW TO FIND IT
Scan an API using Scriptable Request Modifications for custom auth flows.
📍 Configure SRM in the DAST Enterprise policy to handle unique header requirements.
Scan internal applications behind a firewall using Internal Scanning Management.
📍 Enable ISM in the DAST Enterprise mode settings to reach targets behind the corporate firewall.
DAST Enterprise mode is now available for enhanced web application and API security testing Adds support for login scripts, scanner variables, and client certificates in DAST Enterprise authentication configuration Adds Scriptable Request Modifications (SRM) for API scanning in DAST Enterprise Allows uploading or dynamically referencing API specifications in DAST Enterprise Enables scanning of web applications and APIs hosted behind a corporate firewall via Internal Scanning Management (ISM)
5 details in Everything
Veracode DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Adds DAST Enterprise mode to enhance policy enforcement and analytics for web applications and APIs. Adds support for login scripts, scanner variables, client certificates, and Scriptable Request Modifications (SRM) in DAST Enterprise mode. Enables uploading or dynamically referencing API specifications within DAST Enterprise mode. Introduces Internal Scanning Management (ISM) in DAST Enterprise mode to scan apps behind corporate firewalls.
4 details in Everything
Veracode VRM adds Azure DevOps, CrowdStrike CWP, GHAS, JFrog, Qualys connectors and second-party package analysis
Adds Azure DevOps Ticketing connector for bidirectional issue management with Azure DevOps. Adds CrowdStrike Cloud Workload Protection (CWP) connector to ingest runtime threat data. Adds GitHub Advanced Security (GHAS) connector for code and secret scanning secret scanning Checking files, code or other data for exposed credentials such as passwords, API keys and tokens. Findings help teams remove the secret and revoke or rotate it. Adds JFrog Artifactory connector for artifact repository integration. Adds Qualys connector to ingest vulnerability findings from Qualys VM.
+4 more
show less
Enables analysis of Second-Party Packages (internal libraries) within VRM SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment. Adds Column Management for customizing displayed columns in issue and asset tables. Adds Ticketing Metrics tracking for MTTR/MTTA on Jira, ServiceNow, and ADO tickets. Adds Donut charts and Bar charts as new card types for custom dashboards.
9 details in Everything
Updated language and framework support
Mar 27, 2025
· release notes
Veracode adds native scanning support for .NET 9, Apex 61/62, Dart 3.7, Flutter 3.29, and Go 1.24
Adds .NET 9 language/framework profile to enable static analysis of .NET 9 applications Adds Apex 61 and Apex 62 profiles for Salesforce Apex code scanning Adds Dart 3.7 and Flutter 3.29 profiles for Dart/Flutter application analysis Adds Go 1.24 support for Go language static security testing
4 details in Everything
Map multiple domains to a single identity provider
Mar 24, 2025
· release notes
Allows mapping multiple domains to a single identity provider identity provider A service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems. SP-initiated SP-initiated A SAML or OAuth/OIDC login flow where the Service Provider redirects the user to an Identity Provider to authenticate, rather than the IdP pushing an assertion unprompted; tools use it to trigger SSO from their own login page. SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management.
Veracode CLI v2.38.2 adds Go.mod version detection, .NET 9 support, and MSVC warning tolerance for package command.
The veracode package command now identifies the Go version specified in the go.mod file The veracode package command enables builds using Microsoft C++ (MSVC) compilers to succeed even with warning messages The veracode repository add command now supports larger data types (Int64)
3 details in Everything
Veracode CLI v2.38.2 adds --verbose removal, Go version detection, and .NET 9 support
veracode package command now supports identifying the Go version specified in the go.mod fileveracode package command now supports .NET 9veracode repository add command now supports larger data types (Int64)Builds that use Microsoft C++ (MSVC) compilers now succeed, even if there are warning messages
4 details in Everything
Customizable PDF displays SCA Component License Risk policy compliance
Mar 6, 2025
· release notes
Customizable PDFs now display SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Veracode Scan for VS Code v1.13.5 improves C++/Go fix suggestions and adds usage tracking.
└──▷ HOW TO FIND IT
View tracking data for Veracode Fix adoption within your platform analytics dashboard.
📍 Navigate to Veracode Analytics › Veracode Fix Usage
Enhanced Veracode Fix suggestion support for Go projects
1 detail in Everything
Veracode Scan for Visual Studio 2022 v0.4.4
Feb 27, 2025
· release notes
Veracode Scan for Visual Studio 2022 v0.4.4 expands Veracode Fix suggestions to C++ and tracks usage in Analytics.
Enhanced Veracode Fix suggestion support for Go projects Improved logic for matching flaws with code in the editor
2 details in Everything
Updated language and framework support
Feb 27, 2025
· release notes
Veracode updates language and framework support including Rails 8, Angular 18, and improved detection accuracy for C/C++, iOS, and PL/SQL.
Enhanced support for Angular 18 in JavaScript scanning. Added support for Rails 3.4 and Rails 8 in Ruby on Rails scanning. Improved flaw detection for exported functions in C/C++. Improved detection accuracy for taint-based flaws in iOS. Enhanced SQL injection SQL injection An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does.
5 details in Everything
C# API wrapper v25.2.10.2 adds failbuild parameter and Git URL update support
└──▷ USE IT
Ensure CI pipelines fail immediately when application artifact uploads to Veracome fail.
code
copy
var profile = new ApplicationProfile() { GitRepoUrl = "https://github.com/example/repo", FailBuild = true };
Adds the failbuild parameter to the C# API wrapper to fail the build if an artifact fails to upload. Adds support for updating a Git repository URL for an application profile via the C# API wrapper.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! Replaced deprecated XML APIs XML APIs Interfaces for reading, writing, or querying XML documents, provided by libraries such as libxml2 or built into language runtimes; cyber tools use them to parse structured data like configs, reports, or protocol messages reliably.
Veracode CLI v2.38.0 adds --verbose to package and retries failed static scans up to 5 times
└──▷ USE IT
Enable verbose output when packaging an application for analysis
shell
copy
veracode package --app "MyApp" --build "1.0" --path ./dist --verbose
Adds --verbose flag to the veracode package command The veracode static scan command now retries failed scans up to five times on server errors or too many requests
2 details in Everything
Veracode CLI v2.38.0 adds --verbose to package, retries static scans on errors
veracode package now accepts the --verbose flag for detailed outputveracode static scan retries failed scans up to five times on server errors or rate limiting
2 details in Everything
Veracode adds Customer Managed Encryption Keys (CMEK) to allow platform data encryption with customer-owned root keys
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
SCA agent default backend API endpoint changed to https://sca-api.veracode.eu for European region customers. SCA agent default backend API endpoint changed to https://sca-api.veracode.us for United States Federal region customers.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! Legacy URL https://platform-backend.analysiscenter.veracode.eu will be retired after 12 months, requiring config updates for EU customers.! Legacy URL https://platform-backend.analysiscenter.veracode.us will be retired after 12 months, requiring config updates for US Federal customers.
Adds sandbox ID filtering to Findings and Scans reports in Reporting REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Adds support for filtering Findings reports using development sandbox IDs Adds support for filtering Scans reports using development sandbox IDs
2 details in Everything
Updated language and framework support
Jan 27, 2025
· release notes
Veracode adds support for Dart 3.6, Flutter 3.27 and improves flaw detection across multiple languages.
Improved third-party code detection for Java Improved third-party code detection for JavaScript and TypeScript Enhanced overall flaw detection for PHP Improved SQL injection SQL injection An attack that makes an application treat untrusted input as part of a database command. It can expose or modify data by changing what the query does. Improved parsing for PL/SQL
+1 more
show less
Improved parsing for T-SQL
6 details in Everything
Veracode Scan for Visual Studio v0.4.1
Jan 16, 2025
· release notes
Veracode Scan for Visual Studio v0.4.1 adds automatic msbuild detection to fix autopackaging for .NET Framework apps.
Adds automatic detection of msbuild to ensure the autopackager reliably packages .NET Framework applications.
1 detail in Everything
Veracode CLI v2.37.0 adds Windows MSI installer, autopacking for .NET MAUI/Blazor and Azure Functions
Adds .NET MAUI, .NET Blazor WebAssembly, and .publishproj support to the veracode package autopacker. Adds signed Microsoft Standard Installer (MSI) package for Windows installation of the CLI.
2 details in Everything
Veracode CLI v2.37.0 adds Windows MSI installer, progress indicators, and new .NET autopackaging targets.
Adds a signed Microsoft Standard Installer (MSI) file for installing the CLI on Windows Adds --progress indicator display during command execution Expands veracode package autopackaging to cover .NET MAUI framework, .NET Blazor WebAssembly WebAssembly A binary instruction format that runs in browsers and server runtimes at near-native speed, letting developers compile C, Rust, or other languages into a portable, sandboxed module any compliant host can execute. .publishproj file types
3 details in Everything
Veracode Workflow App v0.2.16 for GitHub
Dec 19, 2024
· release notes
Veracode Workflow App v0.2.16 supports scanning multiple artifacts in Pipeline Scan
Veracode Scan for VS Code v1.13.1 adds auto SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds auto SCA scanning option to automatically scan open-source libraries when a project opens or libraries change. Highlights vulnerable libraries in the package manager file after an SCA scan for Maven, npm, or Yarn projects.
2 details in Everything
Updated language and framework support
Dec 17, 2024
· release notes
Veracode adds .NET 8 MAUI, Cobra (Go), iOS 18, NestJS 10.3.x support and improves third-party detection
Adds dotnet framework support for .NET 8 MAUI applications to the static analysis engine. Adds go framework support for the Cobra CLI library in source code analysis. Adds iOS 18 platform support with improved behavioral detection, Foundation, HealthKit, and Swift Memory Management coverage. Improves Java third-party code detection accuracy for existing Java applications. Adds JavaScript framework support for NestJS version 10.3.x.
5 details in Everything
United States Federal region status page
Dec 16, 2024
· release notes
New status page for US Federal region maintenance and incident notifications
Adds a new https://status.veracode.us status page for the United States Federal region
1 detail in Everything
Veracode TeamCity Plugin v2.8.0 adds an Optional Argument field for upload/scan tasks.
└──▷ HOW TO FIND IT
Pass custom upload parameters during CI/CD scanning via the TeamCity plugin.
📍 In the TeamCity build configuration, go to the Veracode Upload and Scan step and enter values in the new Optional Argument field.
Veracode TeamCity Plugin v2.8.0 introduces a new UI field to allow direct input of optional arguments for scans.
Added the Optional Argument field to the Upload and Scan task.
1 detail in Everything
Veracode Scan for VS Code v1.12.0 adds option to skip vulnerable method analysis during SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Veracode Scan for VS Code v1.12.0 adds an option to skip vulnerable method analysis during SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Veracode adds OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against.
Adds OWASP API Top 10 2023 labs training content to the Veracode platform Adds four new lab scenarios: OWASP API 6 (Node), OWASP API 7 (.NET and Node), and OWASP API 10
2 details in Everything
Veracode Fix Action for GitHub v1.0.1
Nov 26, 2024
· release notes
Veracode Fix Action for GitHub v1.0.1 adds additional CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
Adds additional CWE support for single fix and batch fix actions. Removes restriction requiring app as the root folder name in the user codebase.
2 details in Everything
Veracode CLI v2.36.0 adds autopackager resilience for .NET warnings and Ruby gem ignoring.
veracode scan command output generation is improved
1 detail in Everything
OWASP Top 10 2021 labs and OWASP API Top 10 2023 labs
Nov 6, 2024
· release notes
Veracode adds OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against.
Adds four new training lessons for Insufficient Entropy, The Great Referral Quest, Retrieval Without Validation, and Gift Cards at Risk. Introduces More OWASP Vulnerabilities for APIs category for lessons not in the current API Top 10.
2 details in Everything
Updated language and framework support
Oct 31, 2024
· release notes
Veracode adds JDK 23 support for Java scanning and improves flaw detection accuracy.
Adds JDK 23 support for Java static analysis Improves CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. Improves CWE-80 and CWE-601 flaw detection in JavaScript, reducing false positives
3 details in Everything
New VRM features include custom risk remediation dashboards, Okta SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management.
Adds the ability to create custom risk remediation dashboards to visualize application security and issue prioritization. Enables Okta SSO integration for centralized user authentication management. Introduces a ServiceNow connector that leverages the ServiceNow API to create incident or request tickets from VRM issues. Adds Veracode Connector 1.5 support to ingest Veracode AST AST An abstract syntax tree, a structured representation of parsed code. Tools inspect or transform this tree to understand expressions and statements rather than just matching text. Adds Rapid7 and Tenable connectors to import operational vulnerability data from scanned assets.
5 details in Everything
Veracode CLI v2.35.0 introduces capability to package source code for projects without a package manager, ensuring complete code inclusion for Python, JavaScript, and PHP.
Veracode ISM endpoint 24.10.0 adds a configurable proxy exclusion list for bypassing proxy settings.
ISM endpoint 24.10.0 adds a proxy exclusion list for bypassing configured proxy settings.
Veracode CLI v2.34.0 adds cache clearing, secrets detection via policy regex/keywords, and a temp directory config option
└──▷ USE IT
Run a scan using organization policy for secrets detection, failing fast if the policy check is explicitly false.
shell
copy
veracode scan --policy true
Adds the cache subcommand to clear the CLI cache for all commands Enables custom keywords and regex patterns in secrets detection based on the organization's policy using the --policy flag
2 details in Everything
└──▷ BREAKING ON UPGRADE
! If --policy is set to false, the veracode scan command now exits with code 3 instead of its previous behavior.
Veracode CLI v2.34.0 adds cache clearing, custom secrets detection patterns, temp dir support, and policy exit codes
Adds veracode cache command to clear the cache for all commands Adds support for custom keywords and regex patterns in veracode scan based on organization policy for secrets detection Adds ability to define a temp directory in veracode scan Causes veracode scan to exit with code 3 when policy passed is false
4 details in Everything
Veracode Scan for Visual Studio v0.3.0
Oct 15, 2024
· release notes
Veracode Scan for Visual Studio v0.3.0 adds Software Composition Analysis (SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Veracode Fix Action for Github 1.0.0
Oct 10, 2024
· release notes
Adds Veracode Fix as a new GitHub Action (v1.0.0) for reviewing and applying code fixes to flaws.
Custom roles for user accounts and API service accounts
Oct 9, 2024
· release notes
Veracode introduces custom roles for user and API service accounts, enabling precise access control via new Identity API endpoints.
Adds the ability to create, edit, and manage unique, tailored custom roles for user accounts and API service accounts. Adds a new Identity API specification available on SwaggerHub to facilitate role management programmatically.
2 details in Everything
New Scans report available for the Reporting API
Sep 30, 2024
· release notes
Veracode Reporting API now supports querying scan data (Static, Dynamic, Pen Test) via a new Scans report.
Veracode Scan for Visual Studio v0.2.0
Sep 26, 2024
· release notes
Adds Veracode Fix integration enabling AI-generated flaw remediation directly in Visual Studio
Updated language and framework support
Sep 26, 2024
· release notes
Veracode adds Android 15, Rails 7.2, Laravel Blade/Views support and improves analysis accuracy
Adds initial support for Android 15 applications Adds Rails 7.2 framework support for Ruby on Rails scanning
2 details in Everything
Introducing Veracode Scan for Visual Studio v0.1.0
Sep 24, 2024
· release notes
Veracode Scan for Visual Studio v0.1.0 adds SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment.
Veracode CLI v2.32.0 adds PL/SQL and T-SQL package support and a verbose flag for scans.
└──▷ USE IT
Inspect debug output when a scan fails or hangs to identify underlying issues.
shell
copy
veracode scan --api-key $VC_API_KEY_ID:$VC_API_KEY_SECRET --src ./app --verbose
Package legacy database scripts for analysis alongside standard web app code.
shell
copy
veracode package --name my-app --src ./src/db/stored_procedures.sql ./src/web/app.py
veracode package now supports PL/SQL and T-SQL source filesveracode scan accepts --verbose to display debug logsveracode package improved packaging for Python, PHP, .NET (EXE), Windows JavaScript, and iOS gen-ir
3 details in Everything
Veracode CLI v2.32.0 adds --verbose flag to scan command and improves packaging for multiple languages
Adds --verbose flag to the veracode scan command to show debug logs Adds support for PL/SQL and T-SQL in the veracode package command Improves packaging for iOS to support the latest release of gen-ir
3 details in Everything
New status and maintenance REST API endpoint
Sep 13, 2024
· release notes
New REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. GET /api/v2/summary.json for service status and maintenance schedules
└──▷ BREAKING ON UPGRADE
! The old endpoint https://api.status.veracode.com/status will be retired on October 31, 2024; calls to it will fail after that date.
Updated language and framework support
Sep 13, 2024
· release notes
Veracode iOS packaging tool v0.5.0 adds PIF support and Xcode 16 compatibility
Adds PIFSupport library to Gen IR for parsing Project Interchange Format (PIF) from Xcode and SPM Generates new Homebrew formulas for installation and downgrade: veracode/gen-ir@0.4.x Adds support for projects built or generated with Xcode 16
3 details in Everything
Veracode Workflow App 0.2.13 for GitHub
Sep 12, 2024
· release notes
Veracode Workflow App 0.2.13 adds custom runner, image, and dependency configurations for GitHub Actions GitHub Actions GitHub's built-in CI/CD system that runs automated workflows triggered by repository events, letting cyber tools automate testing, building, and releasing without managing separate pipeline infrastructure.
actions:ruby:version config key lets you specify the Ruby version required in your projectactions:ruby:bundle config key allows specifying a specific bundler for gem installationactions:{scan type}:build:runs_on config key defines the runner for building your projectactions:{scan type}:build:packager_image config key enables using a public docker image for buildsactions:{scan type}:build:predependency_command config key supports additional build commands
5 details in Everything
Veracode CLI v2.31.0 adds SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue.
└──▷ TRY IT
Scan a Software Bill of Materials Software Bill of Materials A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue.
copy
$ veracode scan --sbom <path_to_sbom.json>
Adds veracode scan capability to process SBOMs SBOMs A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. Adds proxyUrl parameter to the Veracode CLI installation script for PowerShell to configure proxy servers during installation
2 details in Everything
Introducing Veracode SAST for Eclipse IDE v1.0.0
Sep 9, 2024
· release notes
Introducing Veracode SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment.
Adds Veracode SAST for Eclipse IDE plugin to integrate Static Application Security Testing with the Eclipse IDE Enables automatic code packaging into supported artifacts for Static Analysis via the new plugin's autopackaging feature Provides in-IDE security flaw scanning, detailed results, prioritization, and remediation guidance capabilities
3 details in Everything
Veracode CLI v2.31.0 adds SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
veracode package command improves packaging for JavaScriptveracode package command now excludes nested Go modules when packaging Go projectsveracode scan command has improved logging for .NET projectsveracode scan can now scan SBOMs SBOMs A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. Added the proxyUrl parameter to a CLI installation script for PowerShell
5 details in Everything
Updated language and framework support
Aug 26, 2024
· release notes
Adds Dart 3.5/Flutter 3.24, Angular 17, Kotlin 2.0, Go AWS Lambda support and improved CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
Go AWS Lambda package support Enhanced Apex 60 support Improved CWE-316 flaw detection in .NET
3 details in Everything
New VRM features include Application Risk Heatmap, Universal Connector 1.0, GitLab Repository support, and custom compliance mappings.
Application Security Heatmap provides an at-a-glance view of risk for all applications with drill-down capability to assets, issues, solutions, and score trending.Universal Connector 1.0 enables ingestion of assets and findings from any data source via a straightforward API setup. GitLab Repository Connector adds support for scanning files and logs to identify IaC IaC Infrastructure as Code: the practice of defining and provisioning compute infrastructure through machine-readable config files rather than manual processes, giving cyber tools repeatable, version-controlled environment setup. ECR ECR Amazon Elastic Container Registry, AWS's managed service for storing and distributing Docker and OCI container images, giving cyber tools a private, IAM-gated registry without self-hosting infrastructure. GitLab Ultimate connector integration automatically creates issues from Container and SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment. Veracode Connector now supports a new asset type for application profiles, displaying SAST, DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces. SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
5 details in Everything
Early release: Custom compliance mappings
Aug 16, 2024
· release notes
VRM allows filtering the Issues table by user-defined custom compliance standards.
Enables filtering the Issues table by custom compliance standards defined by the organization Adds out-of-the-box support for CIS CIS A nonprofit that publishes consensus-based configuration benchmarks and controls for hardening operating systems, cloud environments, and software; cyber tools use it as a ready-made compliance baseline. NIST 800-53 NIST 800-53 A catalog of security and privacy controls for U.S. federal information systems, published by NIST. Cyber tools cite it to map their findings or features to a recognized compliance framework.
2 details in Everything
Veracode allows editing multiple apps and filtering in one API request.
Added support for filters when editing applications with the API Updated the API to allow editing of multiple applications in one API request Added group by support for specific fields when listing solutions with the API
3 details in Everything
New capability to save custom filter combinations directly within VRM console filter menus for tables and dashboards.
Adds the ability to save filter combinations directly from the VRM console filter menus without leaving the UI.
1 detail in Everything
Veracode Scan for JetBrains 1.3.1 improves autofix filtering and macOS Rider integration
Veracode Fix restricts suggested fixes to flaws with supported CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
1 detail in Everything
Veracode CLI v2.28.0 adds env var support in configure paths and better static scan error messages
veracode static-scan provides improved error messages distinguishing between missing API credentials and invalid ones
1 detail in Everything
Veracode Workflow App 0.2.7 for GitHub
Jul 23, 2024
· release notes
Veracode Workflow App 0.2.7 adds autopackaging for JavaScript, Python, Go, Scala, Kotlin, React Native, and Android.
Veracode CLI v2.27.1 adds package analysis for C/C++, COBOL, Perl and multiple .NET target frameworks
veracode package now supports scanning C/C++ (Windows) binaries.veracode package now supports scanning C/C++ (Linux) binaries.veracode package now supports scanning COBOL sources.veracode package now supports scanning Perl sources.veracode package now parses *.csproj, Directory.Packages.props, and Directory.Build.props for multiple .NET target frameworks.
5 details in Everything
Veracode CLI v2.27.1 adds C/C++, COBOL, Perl and multi-framework .NET support to package command
Adds veracode package support for C/C++ on Windows and Linux, COBOL, and Perl. Enables veracode package scanning of multiple target frameworks defined in *.csproj, Directory.Packages.props, and Directory.Build.props files. Improves language support for .NET within the package command.
3 details in Everything
Veracode CLI v2.26.0 adds .NET Framework 4.6-4.8 support and improved Flutter/Android/PHP/.NET language handling
Adds support for .NET Framework versions 4.6 through 4.8 in the veracode package command Enables restoration of .NET projects using <TargetFramework> tags within the veracode package command Improves language support for Flutter, Android, PHP, and .NET applications during packaging Provides more meaningful --debug messages when required build or packaging tools are missing
4 details in Everything
Veracode Workflow App 0.2.3 for GitHub
Jun 28, 2024
· release notes
Veracode Workflow App adds .NET autopackager support and clarifies GitHub check run naming.
Adds Autopackager support for .NET repositories GitHub check run names now indicate whether they are pipeline scans or policy scans GitHub check run summary pages now display the Veracode Platform URL regardless of status
3 details in Everything
Veracode CLI v2.26.0 adds .NET Framework 4.6-4.8 support and improved debug messages
New platform support for .NET Framework versions 4.6 through 4.8 Supports restoring .NET projects via the <TargetFramework> property
2 details in Everything
Updated language and framework support
Jun 27, 2024
· release notes
Veracode adds .NET, Apex, COBOL, iOS, Perl, PHP scanning improvements and support for Dart 3.4, Flutter 3.22, Next.js 14.x, Ruby 3.3, Rails 7.1, and Visual Studio 2022 MSVC.
Veracode Scan for JetBrains 1.1.0 adds Veracode Fix AI-generated patches and JetBrains Rider support
Adds Veracode Fix to apply AI-generated fixes directly to flaws from within the IDE
1 detail in Everything
New component metrics added to SCA agent results
Jun 24, 2024
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds commits count to the SCA agent CLI summary and JSON output when scanning a component from a GitHub repository Adds repository stagnancy metric to the SCA agent CLI summary and JSON output for components sourced from GitHub
2 details in Everything
Project scan IDs added to Reporting API
Jun 20, 2024
· release notes
Reporting API now includes original_project_scan_id and latest_project_scan_id in findings reports
Adds original_project_scan_id to Findings report for application-linked findings from agent-based scans
1 detail in Everything
Veracode CLI v2.25.0 adds Alpine support and improves language coverage for veracode package and scan commands
veracode package and veracode scan commands are now supported on alpine-based environments.Improved Java, Javascript, and Python language support for the veracode package command.
2 details in Everything
Veracode for JetBrains 1.0.0 adds Static Analysis (SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment.
Adds Static Analysis (SAST) scanning capability to find flaws in source code directly from the JetBrains IDE. Introduces automatic packaging of code according to Veracode requirements before scanning begins. Provides filtering options to focus on specific static findings and remediation guidance or ignore actions for results.
3 details in Everything
Vulnerabilities and Licenses tabs added to new SCA homepage (Beta)
May 30, 2024
· release notes
The new SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. EPSS EPSS Exploit Prediction Scoring System, an estimate of the probability that a published vulnerability will be exploited in the next 30 days. It helps prioritize investigation and patching. KEV KEV CISA's Known Exploited Vulnerabilities catalog, a list of vulnerabilities with evidence of exploitation in real attacks. It helps teams prioritize fixes for problems attackers already use.
Veracode Scan for VS Code 1.9.2 enables proxy configuration for enterprise network compliance and extends the SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment.
The proxy support option is now generally available in the extension settings Static Analysis scan timeout limit increased to 60 minutes
2 details in Everything
Updated language and framework support
May 23, 2024
· release notes
Veracode updates static analysis with support for Apex 57-60, Stratus VOS COBOL, Scala 3.4, and JDK 21/22.
Adds Apex 57 , Apex 58 , Apex 59 , and Apex 60 framework support for static scanning. Adds Stratus VOS COBOL platform support to the COBOL scanning engine. Adds Scala 3.4 language support for static analysis. Adds enhanced detection for JDK 21 and JDK 22 in Java scanning.
4 details in Everything
Veracode Scan for VS Code 1.9.0 - Pre-release
May 10, 2024
· release notes
Veracode Scan for VS Code 1.9.0 adds proxy server support for authentication.
New columns in SCA License Risk Data Export report
May 6, 2024
· release notes
SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. SPDX SPDX An open standard for describing software components, licenses and their relationships. Its documents let different tools exchange a software bill of materials without inventing a new format.
Adds Business Unit column to the SCA License Risk Data Export report for applications associated with SCA upload scans Adds Project Name column to the SCA License Risk Data Export report for SCA agent-based scanning projects Adds Library Version column to the SCA License Risk Data Export report for libraries found in SCA agent-based scans Adds Last Scanned Date and SPDX ID columns to the SCA License Risk Data Export report for libraries found in SCA agent-based scans or upload scans
4 details in Everything
Exploitability data added to JSON file produced by SCA agent
Apr 30, 2024
· release notes
The SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Veracode Analytics upgrades to Looker 24.0 with new filtering and UI capabilities
Adds AND/OR filtering in the Veracode Analytics dashboard, allowing complex query composition. Introduces a performant field picker for faster metric selection in Visualizations. Enables quick resize and tile repositioning directly within the Looker dashboard interface.
3 details in Everything
Updated language and framework support
Apr 25, 2024
· release notes
Veracode adds GCC 12/13, Dart 3.3, Flutter 3.19, JDK 22, PHP 8.3 support and improved detections for COBOL archives and specific CWEs CWEs A community-maintained list of software and hardware weakness types, maintained by MITRE, that gives cyber tools a standard taxonomy for classifying and communicating vulnerability root causes.
Adds GCC 12 and GCC 13 (RHEL RHEL Red Hat Enterprise Linux, a commercially supported Linux distribution maintained by Red Hat, chosen by cyber tools for its long support lifecycle, certified hardware compatibility, and enterprise deployment prevalence. Adds support for openSUSE Leap version 15 in C/C++ environments Adds Dart 3.3 and Flutter 3.19 language framework support Adds JDK 22 support for Java applications Adds PHP 8.2 and 8.3 language framework support
+10 more
show less
Enables mandatory single-archive upload for COBOL files, removing individual file upload capability Improves third-party library detection in C/C++ projects Improves CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. Reduces false positives for CWE-259 and CWE-798 flaw detection in Spring Boot applications Adds JavaScript cleansers for CWE-80, 93, 113, and 117 vulnerabilities Reduces false positives for CWE-73 detection in JavaScript code Improves Generic modeling which impacts all CWE categories Improves CWE-259 and CWE-798 flaw detection for all languages Improves CWE-416 detection accuracy in iOS applications Enhances third-party library detection specifically for Android projects
15 details in Everything
└──▷ BREAKING ON UPGRADE
! Veracode no longer supports uploading individual COBOL files outside of an archive; all COBOL files must now be submitted in a single archive.
Veracode Vulnerability Database now includes data from Exploit-DB
Apr 17, 2024
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds Exploit-DB data to the Veracode Vulnerability Database for SCA components Exposes new exploitability information in the Findings API response payloads Provides access to exploit intelligence via the SCA Agent Issues APIs
3 details in Everything
Veracode CLI v2.16.0 adds iOS support to veracode package for SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
veracode package command now supports iOS applications in addition to existing languages (Java, JavaScript, .NET, Python, PHP, Scala, Kotlin, Go, Ruby on Rails) for Static Analysis and SCA upload scansveracode package output displays the installed CLI version
2 details in Everything
Veracode Workflow App 0.2.0 for GitHub
Apr 10, 2024
· release notes
Veracode Workflow App for GitHub adds on-demand issue scans, finding-to-issue creation, custom workflows, and repo-level config overrides.
Adds analysis_on_platform flag to enable policy or pipeline scans (default false) Sets analysis_branch to default branch automatically by default Creates sandbox scans on PR open for the source branch; removes sandbox and starts policy scan on merge Excludes mitigated findings from pipeline scan results lists Adds issues flag to trigger on-demand scans on a GitHub Issue
+7 more
show less
Adds create_issue flag to create GitHub Issues from Static Analysis findings Adds create_code_scanning_alerts flag to create GitHub Security code scanning alerts from findings Allows config allowlist in central repo_list.yml file Allows overriding global configs via veracode.yml at source repo root Adds use_custom_workflow flag to use a workflow from the source repo for building artifacts Displays new error annotations for invalid API credentials and missing policy name Autopackages Java projects automatically
12 details in Everything
└──▷ BREAKING ON UPGRADE
! analysis_on_platform flag must now be added to turn on policy or pipeline scans; it is off by default.
Veracode Analytics adds Policy Status field with Conditional Pass value and updated SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds a new Findings Policy Status field that tags findings violating policy but within grace period as Conditional Pass Updates Policy Rule Passed (Yes / No) field logic for SCA findings so they are not reported as No when within grace period SCA Agent-Based Scan Issues page now provides data about the projects and workspaces that generated the issues
3 details in Everything
Adds a new SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. software bill of materials software bill of materials A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue.
Releases the SBOM Scan REST API to upload an SBOM and identify associated library vulnerabilities Enables generation of a new SBOM including scan results in either CycloneDXCycloneDX An open standard for describing software components and their dependencies, vulnerabilities and other supply-chain information. Tools use it to exchange bills of materials and related evidence. SPDXSPDX An open standard for describing software components, licenses and their relationships. Its documents let different tools exchange a software bill of materials without inventing a new format.
2 details in Everything
Learning paths and improved docs search
Apr 3, 2024
· release notes
Veracode adds guided learning paths for onboarding and improved docs search filtering.
Adds Learning paths providing a sequence of videos and documentation to walk through using Veracode products, from preparation to scanning and results review. Introduces an improved search experience in the documentation that helps you more easily search across all documentation and filter the results.
2 details in Everything
Adds OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against.
Adds OWASP API 6: Bad Design Compromises Security (JavaScript) lab Adds OWASP API 7: Jot Down this Key (JavaScript) lab Adds OWASP API 7: Secret Admin (JavaScript) lab Adds OWASP API 7: eXternal Entity Injection (JavaScript) lab Adds OWASP API 7: XML is Always a Challenge (JavaScript) lab
+6 more
show less
Adds OWASP API 8: Own the Database (JavaScript) lab Adds OWASP API 8: Parameterize All the Things (JavaScript) lab Adds OWASP API 8: Bobby Tables (JavaScript) lab Adds OWASP API 9: Unprotected Deployments (JavaScript) lab Adds OWASP API 10: The Importance of Logging and Monitoring (JavaScript) lab Adds OWASP API 10: Logging in the API Infrastructure (JavaScript) lab
11 details in Everything
include_metrics parameter for getWorkspaces API set to FALSE by default
Apr 1, 2024
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. getWorkspaces API defaults to include_metrics=FALSE, reducing payload size and latency; TRUE needed for issue counts.
getWorkspaces API now returns only id, name, projects_count, and site_id by default (when include_metrics is omitted or set to false).getWorkspaces with include_metrics=true now explicitly supports last_scan_date, library_issues_count, vulnerability_issues_count, and total_issues_count fields in the response.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! getWorkspaces responses no longer include last_scan_date, library_issues_count, vulnerability_issues_count, or total_issues_count unless the caller explicitly sets include_metrics=true.
Fix flaws in multiple files in a directory
Mar 29, 2024
· release notes
Veracode CLI fix command now accepts directories to batch-fix flaws across multiple files.
veracode fix command supports directory arguments to apply suggested fixes to multiple source files in a batch
1 detail in Everything
Beta release of a new SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds a New SCA Home (Beta) toggle under Scans & Analysis > Software Composition Analysis in the Veracode Platform UI Adds the Portfolio tab to view applications and workspaces scanned after March 27, 2024 Adds the Components tab to view discovered components from scans run after March 27, 2024
3 details in Everything
Updated language and framework support
Mar 28, 2024
· release notes
Veracode updates language and framework support including Go 1.22, Android 14, and CentOS/RHEL RHEL Red Hat Enterprise Linux, a commercially supported Linux distribution maintained by Red Hat, chosen by cyber tools for its long support lifecycle, certified hardware compatibility, and enterprise deployment prevalence.
Adds Go 1.22 support Adds CentOS/RHEL 9 (x64) support
2 details in Everything
Veracode Scan for VS Code 1.6.0 adds debug support for SAST SAST Static application security testing, analyzing source code or compiled code for vulnerabilities without running the application. It helps developers find problems before deployment. Clear all findings action.
debug option now supports Static Analysis scans, Veracode Fix, and the autopackager
1 detail in Everything
Veracode adds OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against.
Adds OWASP API 1: One ID to Access All Objects lab for JavaScript Adds OWASP API 1: Stronger IDs lab for JavaScript Adds OWASP API 2: Really, Really Bad Passwords lab for JavaScript Adds OWASP API 2: Terrible Password lab for JavaScript Adds OWASP API 3: Bugs in Debug lab for JavaScript
+5 more
show less
Adds OWASP API 3: Revealing Schemas lab for JavaScript Adds OWASP API 4: Slow Down lab for JavaScript Adds OWASP API 4: Brute Force lab for JavaScript Adds OWASP API 4: Denial of Service lab for JavaScript Adds OWASP API 5: Neglected Endpoints lab for JavaScript
10 details in Everything
New include_metrics parameter for getWorkspaces API
Feb 8, 2024
· release notes
getWorkspaces API gains include_metrics param to toggle payload depth.
include_metrics parameter added to getWorkspaces API endpointDefault value for include_metrics changes from TRUE to FALSE on April 1st, 2024
2 details in Everything
└──▷ BREAKING ON UPGRADE
! The default value for the include_metrics parameter in getWorkspaces API calls changes to FALSE on April 1st, 2024, resulting in payloads containing only id, name, projects_count, and site_id
Expands Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
New commands for reporting on repository contributors
Feb 5, 2024
· release notes
Veracode CLI adds veracode repository add and veracode repository report commands for contributor tracking
└──▷ TRY IT
Prepare an import file of developer mappings from accessible repos
copy
$ veracode repository add Audit which developers contributed to each tracked repository
copy
$ veracode repository report
veracode repository add: create an Excel file listing accessible repositories for importing contributing developersveracode repository report: generate a report listing all contributing developers for each repository
2 details in Everything
Updated language and framework support
Jan 25, 2024
· release notes
Adds jsi filetype support in Java; adds openSUSE (x86) v12 and CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. .jsi files to Java scanning.
Added jsi filetype support for Java scanning Added openSUSE (x86) version 12 platform support for C/C++ analysis Added CWE-639 support for COBOL
3 details in Everything
Veracode CLI package command enables Static Analysis autopackaging for Java, JS, and Python.
└──▷ USE IT
Automatically package a Java application for Static Analysis via the CLI.
shell
copy
veracode package --language java <path-to-app>
package subcommand removes manual packaging steps to streamline application security tests
1 detail in Everything
The Veracode CLI now supports autopackaging for Veracode Static Analysis
Jan 18, 2024
· release notes
Veracode CLI adds Static Analysis autopackaging for Java, JavaScript, and Python
Adds the package subcommand to the Veracode CLI to automate application packaging for Static Analysis
1 detail in Everything
getProjectIssues endpoint now accepts all parameters supported by getWorkspaceIssues.
Veracode Vulnerability Database now includes exploit information
Jan 4, 2024
· release notes
The Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. EPSS EPSS Exploit Prediction Scoring System, an estimate of the probability that a published vulnerability will be exploited in the next 30 days. It helps prioritize investigation and patching. KEV KEV CISA's Known Exploited Vulnerabilities catalog, a list of vulnerabilities with evidence of exploitation in real attacks. It helps teams prioritize fixes for problems attackers already use.
New COBOL scanner for Static Analysis
Dec 27, 2023
· release notes
Veracode Static Analysis adds a new COBOL scanner with advanced pattern recognition.
Web application and API scans now support multi-factor authentication
Dec 19, 2023
· release notes
Web application and API scans now support MFA MFA Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. TOTP TOTP A one-time password algorithm (RFC 6238) that generates short-lived codes from a shared secret and the current time, giving cyber tools phishing-resistant second-factor authentication without a server round-trip. REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Adds TOTP seed configuration to web application scans and API scans for URLs requiring multi-factor authentication multi-factor authentication Multi-factor authentication, requiring proof from different categories, such as a password and a hardware key, to sign in. It reduces reliance on a password alone. Enables TOTP configuration for MFA-scanned resources via the REST API
2 details in Everything
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. KEV KEV CISA's Known Exploited Vulnerabilities catalog, a list of vulnerabilities with evidence of exploitation in real attacks. It helps teams prioritize fixes for problems attackers already use.
SCA Agent Issues API now includes fields from the CISA Known Exploited Vulnerabilities CISA Known Exploited Vulnerabilities A catalog maintained by the US Cybersecurity and Infrastructure Security Agency listing CVEs confirmed to have been actively exploited in the wild, which cyber tools use as a high-signal prioritization feed for patching and scanning. Findings API now includes fields from the CISA Known Exploited Vulnerabilities Known Exploited Vulnerabilities CISA's Known Exploited Vulnerabilities catalog, a list of vulnerabilities with evidence of exploitation in real attacks. It helps teams prioritize fixes for problems attackers already use.
2 details in Everything
Updated language and framework support
Dec 14, 2023
· release notes
Veracode adds .NET 8, ES14, Go AWS SDK, Dart/Flutter support and new CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
Added initial support for .NET 8 language analysis Added support for JavaScript / ECMAScript 2023 (ES14) Added Config support from AWS SDK for Go Added Dart 3.2 and Flutter 3.16 support Added detection of CWE-489 (Active Debug Code) in Go
5 details in Everything
Veracode ISM endpoint 23.12.1 adds Java 21 support with virtual threading.
Adds Java 21 platform support to the ISM endpoint Enables virtual threading functionality for improved performance and stability
2 details in Everything
Veracode Azure DevOps Extension 3.25.0
Dec 12, 2023
· release notes
Veracode Azure DevOps Extension 3.25.0 adds fail-build reliability and iteration path overwrite for flaw imports.
Fail build if Upload and Scan build step fails checkbox now reliably triggers build failure in both the Upload and Scan task and the Flaw Import taskAdds an option to overwrite the iteration path in work items of imported flaws during the next import
2 details in Everything
Veracode releases GitHub Workflow App for centralized Static, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Enables automated scanning triggered by developer activity via template workflows without requiring per-repository configuration.
1 detail in Everything
Veracode offers a free 14-day trial of DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Veracode Platform adds a free 14-day trial for Dynamic Application Security Testing (DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Veracio introduces DAST DAST Dynamic application security testing, probing a running application from the outside for vulnerabilities. It checks behavior exposed through the application's interfaces.
Launches a new DAST product for Dynamic Application Security Testing of web applications and REST APIs REST APIs A convention for building HTTP-based interfaces where resources are addressed by URL and manipulated with standard verbs like GET, POST, and DELETE, giving cyber tools a predictable way to integrate with external services.
1 detail in Everything
Updated language and framework support
Nov 15, 2023
· release notes
Veracode adds support for Jakarta EE, Spring Boot/Core 6, Java Records, Android 14, AWS SDK for Go KMS KMS A managed service that creates, stores, rotates and controls access to encryption keys, usually backed by HSMs. Applications ask it to encrypt or decrypt rather than holding keys themselves.
Added Javax to Jakarta transition support Added support for Java Records Added Spring Boot 3 support Added Spring Security 6 support Added Spring Core 6 support
+1 more
show less
Added Android 14 Initial support
6 details in Everything
Veracode SCA Scan for VS Code 1.3.1
Nov 9, 2023
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds security policy filtering to exclude low-importance findings in the project configuration. Adds a link to the related CVE in the Vulnerability Details window UI element. Adds a debug option flag to troubleshoot scan errors during execution.
3 details in Everything
API to propose and approve mitigations for SCA findings
Nov 6, 2023
· release notes
New Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Adds getSCAannotations endpoint to retrieve comments and applied mitigations for SCA upload scans Adds createSCAannotations endpoint to annotate SCA findings, including proposing, accepting, or rejecting mitigations
2 details in Everything
Veracode Integration for Jira Cloud 4.12.0
Nov 1, 2023
· release notes
Veracode Integration for Jira Cloud 4.12.0 adds a retry capability for failed imports and corrects region-specific link behavior and field values.
Adds a retry option on the Import Automation page to redownload Detailed Reports that failed during import Updates application profile links in Jira issues for European accounts to open in the Veracode Platform European region
2 details in Everything
New Veracode Analytics fields available in European Region
Oct 16, 2023
· release notes
Veracode Analytics' Findings explore adds Second Party Component and Fixable fields for EU region users
Second Party Component field added to Veracode Analytics Findings explore results in the European Region.Fixable (Yes / No) field added to Veracode Analytics Findings explore results in the European Region.
2 details in Everything
Exploit probability (EPSS) added to Findings API
Oct 11, 2023
· release notes
Exploit probability (EPSS EPSS Exploit Prediction Scoring System, an estimate of the probability that a published vulnerability will be exploited in the next 30 days. It helps prioritize investigation and patching. REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Updated language and framework support
Oct 2, 2023
· release notes
Veracode adds support for iOS 17, Go 1.21, Laravel 10, and new CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
Adds iOS 17 initial support Adds .NET Minimal API support Adds CWE-566 (Authorization Bypass Through User-Controlled SQL Primary Key) detection for .NET applications
3 details in Everything
Assign policies to SCA agent-based scan workspaces
Sep 22, 2023
· release notes
New Unified Policy feature allows assigning policies to SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
└──▷ BREAKING ON UPGRADE
! Veracode will retire agent rules before April 1, 2024, as part of the migration to Unified Policy.
Agent-based scan UI now displays CVSS v3
Aug 28, 2023
· release notes
Agent-based scan UI now displays CVSS CVSS Common Vulnerability Scoring System, a method for describing a vulnerability's characteristics and severity. Its score is not the probability that attackers will exploit it.
Updated language and framework support
Aug 23, 2023
· release notes
Veracode Static Analysis adds Kotlin 1.9, TypeScript 5.x, and GCC 12 (RHEL RHEL Red Hat Enterprise Linux, a commercially supported Linux distribution maintained by Red Hat, chosen by cyber tools for its long support lifecycle, certified hardware compatibility, and enterprise deployment prevalence.
Adds GCC 12 (RHEL 8) compiler support Enables allowing third-party PHP software when the entire upload is third-party
2 details in Everything
Veracode Azure DevOps Extension 3.23.0
Aug 16, 2023
· release notes
Veracode Azure DevOps Extension adds iteration path to Flaw Importer and supports AZDO 2022 RC2.
Adds iteration_path configuration to the Flaw Importer task for work item settings Adds support for Azure DevOps version 2022 RC2
2 details in Everything
Exploit probability (EPSS) added to SCA Agent APIs
Aug 8, 2023
· release notes
Exploit probability (EPSS EPSS Exploit Prediction Scoring System, an estimate of the probability that a published vulnerability will be exploited in the next 30 days. It helps prioritize investigation and patching. SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. REST APIs REST APIs A convention for building HTTP-based interfaces where resources are addressed by URL and manipulated with standard verbs like GET, POST, and DELETE, giving cyber tools a predictable way to integrate with external services.
Veracode SCA Scan for VS Code 1.2.0
Aug 8, 2023
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Veracode Greenlight for IntelliJ 1.8.8
Jul 28, 2023
· release notes
Veracode Greenlight for IntelliJ 1.8.8 improves stability by resolving exception errors during file/folder scans and adds compatibility with IntelliJ version 1.8.7.
API to retrieve list of SCA agent projects linked to an application
Jul 28, 2023
· release notes
New getApplicationProjects API retrieves SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Veracode adds deps.json/project.asset.json support and --quick flag for .NET SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
SCA upload scans now parse deps.json and project.asset.json to reduce false positives
1 detail in Everything
Introducing Veracode SCA Scan for JetBrains
Jul 21, 2023
· release notes
Introduces Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Veracode SCA Scan for VS Code 1.1.0
Jul 20, 2023
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds project selection when multiple projects are open in VS Code Shows scanned project name in the SCAN OVERVIEW view Adds recursive scanning enable/disable toggle in extension settings
3 details in Everything
Veracode Integration for Jira Server 4.1.0
Jul 6, 2023
· release notes
Veracode Integration for Jira Server 4.1.0 enhances import reliability and visibility.
Import Automation now attempts to re-import flaws that previously failed during an import cycle Troubleshooting page gains a diagnostic dashboard showing details about the latest import including error information
2 details in Everything
Veracode Static for Visual Studio 2019 and 2022 v1.8.0
Jul 6, 2023
· release notes
Veracode Static for VS2019/2022 v1.8.0 adds auto-population of new application details in veracode-project-user.json.
veracode-project-user.json is now automatically updated with details for newly added applications.
1 detail in Everything
Veracode Azure DevOps Extension 3.22.0
Jun 5, 2023
· release notes
Veracode Azure DevOps Extension 3.22.0 adds scan polling interval and static analysis-only flaw import.
Adds scanpollinginterval parameter to the Upload and Scan task to control how often the extension checks for scan completion Allows the Flaw Import task to filter findings by source, enabling imports limited to Static Analysis and SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
2 details in Everything
Adds Show Unstable Status for Failed Policy Evaluation option to control Jenkins job status when scans fail policy checks
Adds a Show Unstable Status for Failed Policy Evaluation option. Select this option to show the job status as Unstable if the scan succeeds but fails the security policy.
1 detail in Everything
Pipeline Scan Adds Support for Module Selection
May 18, 2023
· release notes
Pipeline Scan adds --include parameter to select specific top-level modules
Veracode Azure DevOps Extension 3.21.0
May 4, 2023
· release notes
Veracode Azure DevOps Extension 3.21.0 adds lifecyclestage argument to Upload and Scan task
New Veracode Static Analysis Support for Languages and Frameworks
Apr 27, 2023
· release notes
Veracode adds static analysis coverage for JDK 20, .NET 7, and other tech.
Adds static analysis support for JDK 20. Adds enhanced static analysis support for .NET 7. Adds enhanced static analysis support for Python SQLAlchemy. Adds enhanced static analysis support for React Native 0.7x. Adds static analysis support for AWS SDK for Go v2.
5 details in Everything
Veracode Jenkins Plugin adds STOPPED_VERIFYING_PARTIAL_RESULTS and STOPPED_PARTIAL_RESULTS_AVAILABLE scan status support
Veracode Java API Wrapper adds new dynamic analysis scan statuses and -includenewmodules parameter support
Adds STOPPED_VERIFYING_PARTIAL_RESULTS and STOPPED_PARTIAL_RESULTS_AVAILABLE dynamic analysis scan statuses to the wrapper.
1 detail in Everything
NVD severity ratings for SCA upload scans
Apr 3, 2023
· release notes
SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. NVD NVD The National Vulnerability Database, maintained by NIST, is the U.S. government repository of CVE records enriched with CVSS scores and metadata; cyber tools query it to drive vulnerability prioritization.
New Veracode Static Analysis Support for Languages and Frameworks
Mar 23, 2023
· release notes
Veracode adds static analysis coverage for Vue 3.x, React Native 0.7x, and Python Flask 2.x.
Adds support for Vue 3.x in static analysis. Enhances support for Python Flask 2.x in static analysis.
2 details in Everything
Veracode SCA Scan for VS Code 0.7.0
Mar 20, 2023
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds an installable SCA Agent that can be installed from within the IDE after installing the extension. Groups vulnerabilities in the VULNERABILITIES view by Did Not Pass Policy and Passed Policy . Shows the policy for the selected vulnerability in the Vulnerability Details window.
3 details in Everything
Java API Wrapper adds HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate.
Adds https_proxy environment variable support for configuring proxy host, port, and credentials
1 detail in Everything
Veracode Azure DevOps Extension 3.19.0
Mar 2, 2023
· release notes
Adds YAML support for selecting Azure DevOps Endpoint or Service Connection details via ConnectionDetailsSelection
└──▷ USE IT
Use an existing Azure DevOps Endpoint to authenticate with Veracode in a pipeline task.
yaml
copy
ConnectionDetailsSelection='Endpoint'
Use an Azure DevOps Service Connection to authenticate with Veracode in a pipeline task.
yaml
copy
ConnectionDetailsSelection='Service Connection'
Supports ConnectionDetailsSelection='Endpoint' in pipeline YAML to use an Azure DevOps Endpoint for connection details. Supports ConnectionDetailsSelection='Service Connection' in pipeline YAML to use an Azure DevOps Service Connection for connection details.
2 details in Everything
Veracode Azure DevOps Extension 3.18.0
Mar 1, 2023
· release notes
Extension 3.18.0 updates connection configuration syntax, adds metadata fields to analysis work items, and tightens build failure criteria for dev sandboxes.
└──▷ BREAKING ON UPGRADE
! YAML pipelines must update ConnectionDetailsSelection='Endpoint' to ConnectionDetailsSelection='Service Connection' or fail to configure the connection correctly.
New Manual Resume Feature for Paused Analyses
Feb 17, 2023
· release notes
Veracoda Dynamic Analysis adds manual resume for paused analyses (by request only)
Enables manual resumption of scheduled Dynamic Analysis scans that are in a paused state
1 detail in Everything
New Veracode Static Analysis Support for Languages and Frameworks
Jan 26, 2023
· release notes
Veracode expands its cyber toolchain by supporting .NET 7 and JavaScript SSRF SSRF Server-side request forgery, an attack that tricks a server into making requests chosen by an attacker. Those requests can reach internal services the attacker cannot access directly.
Introducing Veracode SCA Scan for VS Code
Jan 17, 2023
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Enables detection of security risks in open-source libraries and dependencies within the IDE
1 detail in Everything
Improved Veracode Azure DevOps Extension
Jan 5, 2023
· release notes
Veracode Azure DevOps Extension 3.17.0 improves pipeline resilience and workflow control.
Updates the Veracode Analysis Center link to Veracode Platform in the extension UI. Allows pipelines to pass with a Conditional Pass policy assessment without failing when Fail build if application fails security policy is enabled. Enables build failure for the Flaw Import task when importing flaws with an unsupported process template, provided Fail build if flaw importer build step fails is checked.
3 details in Everything
Improved Veracode Integration for Jira Server
Dec 19, 2022
· release notes
Veracode Integration for Jira Server 3.38 adds CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Jira tickets from imported Static Analysis flaws now display detected CWEs CWEs A community-maintained list of software and hardware weakness types, maintained by MITRE, that gives cyber tools a standard taxonomy for classifying and communicating vulnerability root causes. Jira tickets from imported SCA vulnerabilities now support the Mitigation Status and Mitigation Status Description fields.
2 details in Everything
New Veracode Static Analysis Support for Languages and Frameworks
Dec 15, 2022
· release notes
Veracode adds static analysis support for Node.js 18, Laravel 6-9, Kotlin 1.7, Android 13, Flask 2.x, Go 1.18-1.19, React Native 0.67, Dart/Flutter, .NET MAUI, and Xcode 14 v
Adds gen-ir iOS packaging tool to support Xcode 14 without the Enable_Bitcode setting
1 detail in Everything
Veracode for VS Code Renamed to Veracode Greenlight for VS Code
Dec 14, 2022
· release notes
Veracode for VS Code renamed to Veracode Greenlight for VS Code in version 1.6.0
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds support for scanning AAR files in agent-based scans. Adds support for scanning APK and AAB files in upload scans.
2 details in Everything
New Veracode Static Analysis Support for Languages and Frameworks
Nov 17, 2022
· release notes
Veracode adds static analysis support for JDK 19 and Azure Functions v4 for .NET
Veracode Azure DevOps Extension Now Supports Automatic Deletion of Incomplete Sc
Oct 21, 2022
· release notes
Veracode Azure DevOps Extension v3.15.0 adds flags to delete incomplete scans
Adds -deleteincompletescan as an optional argument to automatically delete incomplete scans in your pipeline Adds -deleteIncompleteScan as a YAML property option for the same automatic deletion capability
2 details in Everything
API Scanning Adds Support for Scriptable Request Modification
Oct 18, 2022
· release notes
API Scanning adds scriptable request modification via JavaScript for authenticated requests
Adds the ability to use JavaScript to modify an HTTP request at runtime during authentication with a remote host
1 detail in Everything
New Veracode Static Analysis Support for Languages and Frameworks
Oct 4, 2022
· release notes
Veracode adds iOS 16, .NET 6, JDK 18, Golang Gorilla, and React/React Router static analysis support
New Application Security Platform features available in European Region
Sep 29, 2022
· release notes
CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
CWE Top 25 now reflects the 2022 version in the European RegionIssue vulnerability counts are updated in Analytics in the European Region Sandbox information is now available in the Unsubmitted Scans Report in the European Region
3 details in Everything
Improved Finding Import Performance for Veracode Integration for Jira Cloud
Sep 22, 2022
· release notes
Veracode Integration for Jira Cloud v4.6.0 introduces a selective import filter to optimize sync performance by targeting only modified findings.
Adds a filter in Veracode Integration for Jira Cloud that restricts imports to findings with new scan data, policy changes, or changes to applied mitigations since the last import.
1 detail in Everything
New Veracode Static Analysis Support for Languages and Frameworks
Aug 25, 2022
· release notes
Veracode adds full PHP Symfony 5.x, initial Symfony 6.x, and PL/SQL support for Oracle 19c/21c
Adds full static analysis support for PHP Symfony 5.x applications Adds initial static analysis support for PHP Symfony 6.x applications Adds static analysis support for PL/SQL code targeting Oracle 19c and 21c databases
3 details in Everything
Adds OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against.
Adds API 9 Improper Assets Management - Unprotected deployments (.NET) lab to the OWASP API Security Top 10 training suite Adds API 10 Insufficient Logging & Monitoring - The Importance of Logging and Monitoring (.NET) lab to the OWASP API Security Top 10 training suite Adds API 10 Insufficient Logging & Monitoring - Logging in the API Infrastructure (.NET) lab to the OWASP API Security Top 10 training suite
3 details in Everything
Dynamic Analysis available for European region
Jul 28, 2022
· release notes
Veracode Dynamic Analysis is now available in the European region for customers with a subscription.
Enables dynamic analysis security testing and API testing on public-facing web applications and APIs within the European region.
1 detail in Everything
C# API wrapper adds --debug flag and transaction ID header for uploadandscan.
SBOM API support for SCA agent-based scans linked to application profiles
Jul 22, 2022
· release notes
Adds SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. CycloneDX CycloneDX An open standard for describing software components and their dependencies, vulnerabilities and other supply-chain information. Tools use it to exchange bills of materials and related evidence. SBOMs SBOMs A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue.
Exposes a new SCA Agent REST API endpoint to generate Software Bill of Materials Software Bill of Materials A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. The generated SBOM output is formatted in CycloneDX JSON.
2 details in Everything
Veracode Azure DevOps Extension Now Supports Importing SCA Vulnerabilities as Wo
Jul 20, 2022
· release notes
Veracode Azure DevOps Extension v3.13.0 adds SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Flaw Importer task now supports importing Software Composition Analysis (SCA) vulnerabilities as Azure DevOps work items.
1 detail in Everything
Updated Single Sign-On and Just-In-Time Provisioning
Jun 28, 2022
· release notes
Veracode adds new SSO SSO Single sign-on, using one identity provider to sign in to multiple applications. It reduces separate passwords and centralizes account and access management. JIT JIT A runtime compilation strategy where code is translated from an intermediate form to native machine instructions at execution time, giving tools the speed of compiled code without sacrificing dynamic flexibility.
Improved Finding Import Performance for Veracode Integration for Jira Server
Jun 27, 2022
· release notes
Veracode Integration for Jira Server v3.35.0 introduces performance improvements via an incremental import mechanism.
New filter imports only findings with new scan data, policy changes, or mitigation updates.
1 detail in Everything
Updated Veracode Static for Visual Studio (New)
Jun 8, 2022
· release notes
Veracode Static for Visual Studio 1.5.0 adds custom scan naming and XML result import
Change the scan name from the auto-generated value to a custom labelImport and review XML scan results from Veracode Detailed Reports
2 details in Everything
Generate SBOMs for SCA agent-based scans with the REST API
Jun 6, 2022
· release notes
REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. CycloneDX CycloneDX An open standard for describing software components and their dependencies, vulnerabilities and other supply-chain information. Tools use it to exchange bills of materials and related evidence. SBOMs SBOMs A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds the ability to generate a Software Bill of Materials Software Bill of Materials A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue.
1 detail in Everything
SCA dashboards available in Analytics
May 10, 2022
· release notes
SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds predefined SCA Findings dashboard to Veracode Analytics in the European Region Adds Findings , SCA Agent-Based Scans , and SCA Agent-Based Scan Issues data explores to Veracode Analytics
2 details in Everything
Sandbox Information Available in Unsubmitted Static Scans Data Export
May 10, 2022
· release notes
Unsubmitted Static Scans data export now includes sandbox information.
SBOM API support for promoted sandbox scans
May 9, 2022
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. CycloneDX CycloneDX An open standard for describing software components and their dependencies, vulnerabilities and other supply-chain information. Tools use it to exchange bills of materials and related evidence. SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue.
Upload and Scan table loads faster after removing Number of Known Vulnerabilities by Severity column
The Security Training Team Released Seven Labs
May 4, 2022
· release notes
The Security Training Team released seven new security training labs covering OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against.
Adds API3:2019 Excessive Data Exposure - Bugs in Debug (.NET) lab Adds API3:2019 Excessive Data Exposure - Revealing Schemas (.NET) lab Adds API4:2019 Lack of Resources and Rate Limiting - Slow Down (.NET) lab Adds API4:2019 Lack of Resources and Rate Limiting - Brute Force (.NET) lab Adds A04:2021 Insecure Design - Making Secure Decisions (.NET) lab
+2 more
show less
Adds 'A08:2021 Software and Data Integrity Failures - Sleeping With the Enemy (.NET, Node)' lab Adds A10:2021 Server-Side Request Forgery - Get There From Here (Java) lab
7 details in Everything
Java API Wrapper Has Improved -deleteincompletescan Parameter
May 4, 2022
· release notes
Veracode Java API Wrapper v22.5.10.0 updates the behavior of the -deleteincompletescan parameter for the uploadandscan action to support integer status codes.
└──▷ BREAKING ON UPGRADE
! The -deleteincompletescan parameter is no longer backward compatible; existing boolean values must be changed to accepted integer values for the uploadandscan action.
New Status Messages for Partial Scan Results
Apr 28, 2022
· release notes
Dynamic Analysis provides status messages for partial scan results caused by errors, early stops, or duration limits.
Adds new Dynamic Analysis status messages that explicitly indicate when Veracode is verifying partial results and when those results are available for review
1 detail in Everything
Generate SBOMs for SCA upload scans with the REST API
Apr 26, 2022
· release notes
New REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. CycloneDX CycloneDX An open standard for describing software components and their dependencies, vulnerabilities and other supply-chain information. Tools use it to exchange bills of materials and related evidence. SBOMs SBOMs A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue. SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds the ability to generate an SBOM SBOM A software bill of materials, an inventory of the components and versions inside an application. It helps teams find affected software when a dependency has a vulnerability or licensing issue.
1 detail in Everything
Introducing New Veracode Static Extensions for Visual Studio 2019 and 2022
Apr 15, 2022
· release notes
Veracode Static for Visual Studio v1.4.0 adds VS 2022 support and a new Summary View grid.
Adds Veracode Static for Visual Studio extension for Visual Studio 2022 (version 1.4.0) Adds a new Summary View grid in the Veracode Static extension for reviewing and managing findings Adds support for policy and sandbox scans within the Visual Studio extension workflow
3 details in Everything
Veracode Greenlight Now Supports the New Visual Studio 2019 and 2022
Apr 12, 2022
· release notes
Veracode Greenlight extension now supports Visual Studio 2019 and 2022
Dynamic Analysis Adds Support for Concurrent Browsers Running Dynamic Analysis S
Mar 10, 2022
· release notes
Veracode Dynamic Analysis now supports specifying up to 12 concurrent browsers for parallel scans.
Adds support for configuring up to 12 concurrent browsers in dynamic analysis scan settings Enables running multiple dynamic analysis scans simultaneously
2 details in Everything
API Scanning Adds OAuth 2.0 Authentication and Analysis History Options
Mar 8, 2022
· release notes
API Scanning now supports OAuth 2.0 OAuth 2.0 An open authorization framework (IETF RFC 6749) that lets a service grant limited API access to a third party without sharing credentials, giving cyber tools a standard way to authenticate against external platforms.
Adds the ability to configure OAuth 2.0 authentication for API endpoints in specifications, supporting Client Credentials and Password Credentials grant types
1 detail in Everything
JSON output for agent-based scans includes CVSS v3 score
Jan 20, 2022
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. CVSS CVSS Common Vulnerability Scoring System, a method for describing a vulnerability's characteristics and severity. Its score is not the probability that attackers will exploit it.
Adds the cvss_score_v3 field to JSON CLI output for agent-based scans
1 detail in Everything
Veracode European Region now available
Oct 20, 2021
· release notes
Veracode launches a new European Region providing localized data residency for Static and SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Launches a dedicated Veracode European Region for new customers to ensure European data residency. Adds support for Veracode Static Analysis in the new European Region. Adds support for Veracode Software Composition Analysis (SCA) in the new European Region.
3 details in Everything
Veracode Greenlight for IntelliJ Supports Additional IntelliJ IDEA Versions
Oct 18, 2021
· release notes
Veracode Greenlight for IntelliJ v1.7.0 adds support for IDEA 2019.3–2021.2.3
Veracode improves static analysis heuristics for credentials and sensitive data detection.
Improves recognition of password keywords within concatenated strings. Enhances heuristics for identifying potentially sensitive data.
2 details in Everything
Improved Veracode Onboarding Experience
Jul 20, 2021
· release notes
Improved onboarding with new Getting Started with Veracode guidance in the Resource Center
Adds a guided walkthrough of products and training offerings accessible via Resource Center > Getting Started
1 detail in Everything
Veracode Integration for Jira Supports the Jira Select List Field Type for Multi
Jun 23, 2021
· release notes
Veracode Integration for Jira v3.30.0 adds support for the Jira Select List (multiple choices) field type.
Veracode Integration for Jira Cloud Supports the Select List Field Types
May 18, 2021
· release notes
Veracode Integration for Jira Cloud v3.7.0 adds Select List field mapping
Automated User Progress Notifications
Apr 27, 2021
· release notes
Veracode Security Labs now supports automated email notifications for campaign progress and incomplete lab reminders with customizable schedules and messages
Enables automated email notifications in Veracode Security Labs to inform managers of team progress and remind users of incomplete labs Allows defining custom schedules and message content for each notification type
2 details in Everything
Java API Wrapper Adds Parameter for Deleting Incomplete Scans Automatically
Apr 22, 2021
· release notes
Veracode Java API Wrapper adds deleteincompletescan parameter to auto-delete failed scans
Adds deleteincompletescan parameter for automatically deleting scans that did not complete due to one or more errors
1 detail in Everything
Access the Veracode Community from the Veracode Platform
Apr 8, 2021
· release notes
New UI integration allows direct access to the Veracode Community from within the Veracode Platform without a separate login.
Evaluation Timeframe for Security Policies
Apr 7, 2021
· release notes
Veracode's security policy engine now supports temporal filtering of findings, allowing administrators to define start and end dates for compliance evaluation.
Improved Veracode Static Analysis Support for Android Applications
Apr 6, 2021
· release notes
Adds support for analyzing Android applications packaged as Android App Bundles (AAB) in static analysis.
New Analytics Dimension for Findings and Scans
Mar 26, 2021
· release notes
New Analytics filter for archive status allows finding deleted findings and scans
Improved User Management in The Veracode Platform
Mar 22, 2021
· release notes
Veracode Platform adds search by name, email, username, or API ID for user management
Continuous Learning Paths in Security Labs
Mar 4, 2021
· release notes
Veracode adds continuous learning paths in Security Labs that auto-assign next campaigns.
Security Labs now supports continuous campaigns , automatically assigning the next learning path after a user completes their current one.
1 detail in Everything
Enable Team-Based Competition in Security Labs
Mar 4, 2021
· release notes
Veracode introduces team competition capabilities in Security Labs, allowing leaderboards to display collective scores by user role.
Veracode Jenkins Plugin No Longer Encrypts Non-Sensitive Data for Build Jobs
Feb 23, 2021
· release notes
Veracode Jenkins Plugin v21.2.12.0 stops encrypting non-sensitive data in build job config.xml.
Removes encryption of non-sensitive fields stored in the config.xml file for build jobs.
1 detail in Everything
New Static Analysis Findings Information in Veracode Analytics
Feb 9, 2021
· release notes
Veracode Analytics adds function name, class path, and line number details for static analysis findings.
Updated Veracode Azure DevOps Extension
Feb 5, 2021
· release notes
Veracode Azure DevOps Extension 3.4.0 adds YAML pipeline configuration, work item imports with comments, and analysis timeout controls.
Adds support for adding Veracode analysis to build pipelines via YAML configuration Enables importing findings as work items into Azure DevOps using YAML Includes mitigation and annotation comments when importing new findings as work items Allows setting a timeout to fail the build if Veracode analysis does not complete within a specified time
4 details in Everything
New Veracode Static Analysis Support
Feb 4, 2021
· release notes
Veracode adds static analysis support for GCC 9/RedHat 8 C++, Koa.js 2.13, Hibernate 5, and Autofac
Adds support for scanning C++ applications built with GCC 9 on RedHat 8 Adds support for scanning Koa.js version 2.13 Adds support for scanning Hibernate framework version 5 Adds support for scanning Autofac framework in .NET applications, which may result in additional findings
4 details in Everything
Improved Email Notifications for Expiring API Credentials
Jan 19, 2021
· release notes
Veracode sends email notifications for expiring API credentials that now display the API username.
Pipeline Scan Integration with Veracode Security Policies
Jan 7, 2021
· release notes
Pipeline Scan integration with Veracode Security Policies enables consistent policy enforcement.
Veracode Static for IntelliJ Supports Mitigation Proposals in TSRV Format
Dec 17, 2020
· release notes
Veracode Static for IntelliJ 3.2.1 adds support for submitting mitigation proposals in the TSRV format.
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds support for agent-based scans of Debian Docker containers via CLI or CI pipelines Extends Veracode Software Composition Analysis to cover Debian container workloads
2 details in Everything
Veracode Java Wrapper Provides Improved Diagnostic Information
Dec 11, 2020
· release notes
Veracode Java Wrapper v20.12.7.3 adds debug parameter for improved diagnostic information
Provides improved diagnostic information available via the new debug flag in version 20.12.7.3
1 detail in Everything
New REST APIs for Findings, Development Sandboxes, and Summary Reports
Dec 11, 2020
· release notes
New REST APIs REST APIs A convention for building HTTP-based interfaces where resources are addressed by URL and manipulated with standard verbs like GET, POST, and DELETE, giving cyber tools a predictable way to integrate with external services.
Adds Annotations API for commenting on findings and proposing, accepting, and rejecting mitigations Adds Development Sandbox API for creating, updating, and deleting sandboxes Adds Additional Findings APIs for obtaining detailed findings information and generating Summary Reports
3 details in Everything
Additional SCA Details Available from the Findings REST API
Dec 7, 2020
· release notes
Veracode Findings REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services. scan_type and dependency_type fields for SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Allows filtering Findings by scan type (agent-based vs upload) and dependency type (direct vs transitive)
1 detail in Everything
Dynamic Analysis search now supports filtering by target URL for faster scan identification.
Adds the ability to search for individual URL scans in Dynamic Analysis, allowing users to identify which scans are associated with a specified URL.
1 detail in Everything
Expanded Secure Cookie Attributes List
Nov 24, 2020
· release notes
Dynamic Analysis expands the list of recognized secure cookie attributes (SameSite, Secure, HttpOnly) for flaw detection.
Veracode Dynamic Analysis now recognizes an expanded set of known secure cookie attributes including SameSite, Secure, and HttpOnly when checking web applications.
1 detail in Everything
Veracode enhances its Findings REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Adds ability to retrieve the expiration date of the remediation grace period for findings that violate a security policy. Adds ability to filter findings by those with comments or mitigations added after a specific date.
2 details in Everything
Docker Hub Images for the Java API Wrapper, the Python Authentication Library, a
Nov 19, 2020
· release notes
Veracode expands distribution channels by offering its Java API wrapper, Python authentication library, and Pipeline Scan tool as official Docker Hub container images.
Docker Hub image for the Java API wrapper. Docker Hub image for the Python Authentication Library supporting HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it.
2 details in Everything
Veracode Integration for Jira Cloud Improves Findings Import Options
Nov 19, 2020
· release notes
Veracode Integration for Jira Cloud v3.5.0 adds SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Uses mapped custom fields in the Veracode Platform when assigning issues of imported findings
1 detail in Everything
Veracode Static for Eclipse Now Supports Mitigation Proposals in TSRV Format
Nov 19, 2020
· release notes
Veracode Static for Eclipse v3.5.0 adds TSRV-format mitigation proposal submission.
Adds support for submitting mitigation proposals in the Technique, Specifics, Remaining Risk, and Verification (TSRV) format within Eclipse.
1 detail in Everything
Improved Notifications for Delayed Scan Results
Oct 29, 2020
· release notes
Improved notifications and UI indicators for delayed scan results
Adds additional details and links to email notifications for scans that are delayed. Indicates delayed scans under investigation within the Veracode Platform UI.
2 details in Everything
eLearning now supports multi-curriculum assignment, seven new LC courses, and centralized Admin > eLearning page with filtering.
Adds ability for administrators to assign a single learner to multiple eLearning curricula Adds seven new Secure Coding Foundation courses to learner level 1 Adds a Date Started column to the eLearning report for learners Centralizes all eLearning administration actions under Admin > eLearning page, removing settings from Admin > Manage Users Removes eLearning fields from the SAML SAML A standard for passing signed identity assertions between a sign-in provider and an application. It lets a user sign in through their organization's identity provider.
5 details in Everything
Improved Veracode Static Analysis Results
Oct 29, 2020
· release notes
Veracode Static Analysis improves coverage for Angular, JS, Python and others; Pipeline Scan adds filtered JSON failure reports.
JSON format output for the list of issues causing a Pipeline Scan to failStatic analysis support for Apache Commons Static analysis support for AWS SDK for Java Static analysis support for Angular templates Static analysis support for JavaScript
+1 more
show less
Static analysis support for Python
6 details in Everything
Set Default Branch to the Most Recently Scanned Branch or Tag
Oct 15, 2020
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Vulnerable Method Support for JavaScript
Oct 13, 2020
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Install Veracode Greenlight for VS Code to Run Greenlight Scans
Oct 6, 2020
· release notes
Veracode introduces a new VS Code extension for running Greenlight scans directly within the editor.
Adds Veracode Greenlight for VS Code extension available via the Visual Studio Marketplace to enable in-editor scan execution
1 detail in Everything
Veracode adds agent-based Container Scanning for Ubuntu Docker images via CLI and CI pipelines.
Introduces Veracode for GitHub integration with preconfigured GitHub Actions GitHub Actions GitHub's built-in CI/CD system that runs automated workflows triggered by repository events, letting cyber tools automate testing, building, and releasing without managing separate pipeline infrastructure.
Adds Veracode for GitHub as a new integration enabling static analysis via GitHub Actions Preconfigures GitHub Actions to upload code to Veracode for static analysis Enables running pipeline scans from within the GitHub development workflow
3 details in Everything
Shareable Links to Your Analytics Dashboards
Sep 26, 2020
· release notes
Adds shareable links for Analytics dashboards (Org-created and Veracode-standard) in the Veracode Platform.
Adds ability to generate and share direct links to Veracode standard analytics dashboards Adds ability to generate and share direct links to organization-created analytics dashboards
2 details in Everything
Updates to Some XML API Deletion Calls
Sep 26, 2020
· release notes
XML API delete endpoints now return HTTP 200 with change summaries on success
deleteuser.do, deleteteam.do, deleteapp.do, and removefiles.do XML API calls now return an HTTP 200 response and a change summary on successful deletion, replacing the previous behavior of returning a list of remaining items.
1 detail in Everything
└──▷ BREAKING ON UPGRADE
! The deleteuser.do, deleteteam.do, deleteapp.do, and removefiles.do XML API calls no longer return a list of remaining items after deletion; callers expecting that response format will break.
Grace Periods for SCA Policy Rules
Sep 26, 2020
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds the ability to define grace periods for Software Composition Analysis (SCA) upload scans within application security policies. Allows configuring a single grace period that applies to all scan types, including SCA. Enables defining a grace period specifically scoped to SCA scans.
3 details in Everything
Veracode adds a full history export and a 90-day activity log window for application profiles, scans, and sandboxes
Adds the ability to download a report of the full history of application profile activity, scan activity, and sandbox activity Extends the activity log display to show activity data for the past 90 days
2 details in Everything
Rolling sandbox retention limit of 15 scans
Veracode Integration for Jira Cloud Adds Description Field Override Option
Sep 11, 2020
· release notes
Veracode Integration for Jira Cloud 3.4.0 adds a global option to override the Description field in imported issues.
Adds jira.description.override as a global configuration key to replace the Jira issue Description content Enables custom text injection into Jira issue descriptions during finding import
2 details in Everything
Veracode Static Analysis Recognized Cleansers
Sep 1, 2020
· release notes
Veracode Static Analysis adds support for new CRLF cleansing functions.
Adds several new CRLF cleansing functions to the supported list. Removes specific HTML escaping functions (e.g., htmlEscapeAllowEntities, escapeAttribute) from the recognized cleansers list.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! Veracode no longer recognizes com.google.gwt.safehtml.shared.SafeHtmlUtils.htmlEscape as a CRLF cleansing function.! Veracode no longer recognizes org.springframework.web.util.HtmlUtils.htmlEscape as a CRLF cleansing function.
Security Labs adds automatic platform account creation and a new assignment creation wizard.
Integration with the Veracode Platform automatically creates Security Labs accounts for users with the Security Labs User role and grants administrator permissions to those with the Administrator role. New Assignment Creation wizard on the Assign Content page provides suggested lab assignments based on a focus such as Beginner/Intermediate/Advanced, PCI PCI A hardware bus standard that connects peripheral devices to a computer's motherboard; cyber tools targeting hardware-level forensics or memory analysis use it to access device registers and DMA regions directly. New Scala labs for the OWASP OWASP A nonprofit foundation that publishes open standards, guides, and ranked vulnerability lists—most famously the OWASP Top 10—giving cyber tools a vendor-neutral benchmark to test or report against.
3 details in Everything
Changes to deletesandbox.do and deletebuild.do XML API Calls
Aug 29, 2020
· release notes
Veracode API deletebuild.do and deletesandbox.do return summaries on success
deletebuild.do now returns HTTP 200 with a summary of deleted items instead of remaining items
1 detail in Everything
All Applications Page Now Available to Mitigation Approver and Delete Scans Role
Aug 29, 2020
· release notes
All Applications page now accessible to Mitigation Approver and Delete Scans roles
Veracode introduces Findings API v2 for accessing open and mitigated findings.
Adds Findings API Version 2 REST endpoint for querying open and mitigated findings. Enables access to findings from Static Analysis, Dynamic Analysis, Manual Penetration Testing, and Software Composition Analysis scans via the new API.
2 details in Everything
Veracode ISM endpoint 20.8.5 adds proxy hostname bypass and non-default network interface support
Adds veracode.proxy.resolveHostnames property to allow not resolving hostnames for the ISM gateway via proxy, enabling strict outbound HTTPS HTTPS HTTP carried over an encrypted TLS connection. It protects traffic in transit and lets a browser verify the server's certificate. Adds veracode.scanUrlProxy.resolveHostnames property to prevent hostname resolution when accessing scanned URLs via proxy, simplifying configuration by avoiding external sites like Okta. Adds veracode.networkInterface endpoint property to specify a non-default network interface, with the ability to list available interfaces.
3 details in Everything
Adds --gl_issue_generation and --gl_vulnerability_generation flags to Veracode pipeline scan for automated GitLab issue creation.
Adds new GitLab examples in the pipeline scan README and Veracode Help Center
1 detail in Everything
Veracode C# API Wrapper Supports the Veracode API Credentials File
Jul 28, 2020
· release notes
Veracode C# API Wrapper v20.7.8.0 adds support for external credentials file and -credprofile flag.
Adds -credprofile argument to select a named profile from the Veracode API credentials file Makes -vid and -vkey optional in favor of reading credentials from an external file
2 details in Everything
Veracode Java API Wrapper Supports the Veracode API Credentials File
Jul 23, 2020
· release notes
Version 20.7.7.0 of the Veracode Java API Wrapper introduces support for storing API credentials in an external file, enhancing security by avoiding command-line exposure.
The -credprofile parameter allows selection of a credential profile from an external file. Existing -vid and -vkey parameters are now optional.
2 details in Everything
Default Date Limit Applied to Scan Data in Agent-Based Scan Workspaces
Jul 17, 2020
· release notes
Agent-based scan workspaces now default to a 30-day data window for performance.
Advanced License Risk Management for Agent-Based Scans
Jul 7, 2020
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds configurable rules to control acceptable open-source library risk in agent-based scans based on Veracode license risk ratings. Enables rejection of specific licenses during agent-based scan processing.
2 details in Everything
Improved Veracode Static Analysis Support
Jul 1, 2020
· release notes
Improved Veracode Static Analysis covers Boto3 Boto3 The official AWS SDK for Python, maintained by Amazon, that gives tools programmatic access to AWS services like S3, EC2, and IAM through a clean Python API.
Adds static analysis support for AWS SDK for Python (Boto3). Enables additional security checks for applications built using Java 12, 13, and 14. Enables additional security checks for applications built using .NET Core 3.1. Enables additional security checks for applications using Apache Commons libraries. Enables additional security checks for applications using Go templates.
+1 more
show less
Expands iOS scan coverage to analyze standalone frameworks, extensions, and watchOS extensions via module selection.
6 details in Everything
New Accept the Risk Mitigation Type
Jun 29, 2020
· release notes
New acceptance-of-risk mitigation workflow
Enhancements to eLearning Curriculum Creation
Jun 27, 2020
· release notes
eLearning Curriculum UI now shows course length and description with required-checkbox option
Adds length and description fields to the eLearning curriculum creation UI for each course Adds a checkbox in the eLearning curriculum creation UI to mark selected courses as required
2 details in Everything
Veracode Integration for Jira Improves Issue Assignment of Imported Findings
Jun 25, 2020
· release notes
Veracode Integration for Jira v3.24.0 allows mapping Veracode custom fields to Jira fields during issue assignment.
Adds the ability to map Veracode Platform custom fields to Jira fields for imported findings in the veracode-integration-for-jira v3.24.0 release
1 detail in Everything
Introducing Veracode for AWS CodeStar
Jun 25, 2020
· release notes
Veracode for AWS CodeStar v1.0.0 adds Static Analysis and SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds Veracode Static Analysis as a configurable build stage in AWS CodePipeline Adds Veracode Software Composition Analysis (SCA) as a configurable build stage in AWS CodePipeline
2 details in Everything
New API Endpoints for Agent Management
Jun 17, 2020
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Adds the ability to create and delete Veracode SCA Agents via REST API
1 detail in Everything
Veracode Analytics Provides Ignored Issue SCA Data
Jun 16, 2020
· release notes
Veracode Analytics exposes SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Veracode Jenkins Plugin Now Open Source and on Jenkins Marketplace
Jun 16, 2020
· release notes
Veracode Jenkins Plugin v20.6.10.0 released open-source on the Jenkins Marketplace.
New Veracode Static Analysis Support
Jun 13, 2020
· release notes
Veracode enhances static analysis capabilities by extending framework and SDK coverage for Go and JavaScript environments.
New Veracode Static Analysis Support includes improved analysis of Go applications by adding support for the Gorilla framework.New Veracode Static Analysis Support improves analysis of JavaScript applications using AWS Lambda by adding support for the AWS SDK.
2 details in Everything
Improved Veracode Static Analysis Support
Jun 13, 2020
· release notes
Improved static analysis for iOS, .NET, Java, and Go submissions in Veracode.
Improves static analysis of iOS applications to better focus results on custom first-party components rather than third-party libraries. Improves static analysis of .NET and Java applications to more accurately report the analysis size of dependent modules, potentially resulting in smaller reported sizes for scan submissions. Enables reading the go.mod file contents from an application submission to more accurately identify which Go components to analyze.
3 details in Everything
New Dynamic Analysis Dimensions Available in Veracode Analytics
Jun 11, 2020
· release notes
Veracode Analytics adds Path and Vulnerable Parameter fields for Dynamic Analysis results.
Adds Path field to Dynamic Analysis data in Veracode Analytics. Adds Vulnerable Parameter field to Dynamic Analysis data in Veracode Analytics.
2 details in Everything
New Sandbox Attributes Added to Veracode Analytics
Jun 11, 2020
· release notes
Veracode Analytics adds sandbox usage attributes including expiration dates and auto-recreate configuration status.
Enables viewing sandbox expiration dates in the analytics view Shows whether sandboxes are configured for automatic recreation after expiration
2 details in Everything
Crawl Script Support for Comprehensive Scans
Jun 11, 2020
· release notes
Veracode adds support for prerecorded Selenium crawl scripts in Dynamic Analysis scans.
SCA Agent Data Available in Veracode Analytics
Jun 8, 2020
· release notes
Veracode Analytics adds SCA Agent Issues and SCA Agent Scans explores for agent data
Adds SCA Agent Issues explore to Veracode Analytics for tracking SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. Adds SCA Agent Scans explore to Veracode Analytics for tracking SCA agent scan data
2 details in Everything
New Screenshot Verifications and Scan Notes Features
Jun 8, 2020
· release notes
Veracode Dynamic Analysis adds Verification Screenshots and Scan Notes sections to Prescan/Scan Details pages for troubleshooting.
Adds Verification Screenshots section to Prescan Details and Scan Details pages showing engine-captured screenshots at predetermined points Adds Scan Notes section to Prescan Details and Scan Details pages containing engine observations on runtime issues or configuration best practices
2 details in Everything
Veracode Dynamic Analysis scan engine improves coverage for SQL Injection and reports SSL SSL A cryptographic protocol for encrypting network connections, now deprecated in favor of TLS but whose name persists colloquially. Cyber tools reference it when handling HTTPS or other encrypted-channel inspection and termination.
Improved scan engine coverage for CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. Dynamic Analysis scan engine now reports use of Cipher Block Chaining (CBC) ciphers and key exchange algorithms without perfect forward secrecy Updated description and remediation text for SSL issues
3 details in Everything
Bulk Actions for eLearning Administrators
Jun 2, 2020
· release notes
Adds bulk actions for eLearning administrators to assign users to tracks or enable automatic track extensions.
Enables Veracode eLearning administrators to apply assigning learners to tracks/curricula and enabling automatic track extensions to multiple users at once.
1 detail in Everything
Veracode Integration for Jira Cloud Adds Findings Import Options
May 29, 2020
· release notes
Veracode Integration for Jira Cloud 3.3.0 adds options to auto-assign findings to epics and map data types.
Adds the ability to automatically assign imported Veracode findings to a Jira Cloud epic or link them to a related issue Adds mapping of string, number, and date/time data types from Veracode fields to corresponding text, number, and date/time field types in Jira Cloud issues
2 details in Everything
Issue Summary for Agent-Based Scans
May 28, 2020
· release notes
New Issue Summary table added to agent-based scan workspaces in Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Veracode Greenlight for IntelliJ Supports IntelliJ 2020.1
May 28, 2020
· release notes
Veracode Greenlight for IntelliJ v1.5.3 adds IntelliJ 2020.1 support and API credential storage in an external file
Enhanced Access Control for ISM Endpoints
May 26, 2020
· release notes
ISM supports configurable support engineer access duration (days or indefinite) in the console.
Adds the ability to grant Veracode support engineers access to ISM endpoints for a specific number of days (up to 30) in addition to the existing indefinite option. Retains the capability to allow support access indefinitely until explicitly disabled by the user.
2 details in Everything
Client Certificate Authentication Support
May 21, 2020
· release notes
Veracode's Dynamic Analysis capability now expands its operational surface to include client certificate-based authentication, allowing scans of protected endpoints that previously required manual handling or could not be accessed. This is a new integration method rather than a vulnerability check update.
Veracode Dynamic Analysis exposes richer scan status details for network failures and timeouts in All Analyses and Summary pages.
Adds more detailed status information when scans stop due to network issues or because they exceeded the allocated scan duration time Enriches status fields and columns on the All Analyses, Dynamic Analysis Summary, and URL Scan Summary pages with improved end-user visibility
2 details in Everything
Engine JSON Web Token and Obsolete JavaScript Support
May 21, 2020
· release notes
Veracode adds JWT JWT An open standard (RFC 7519) for encoding claims as a signed, optionally encrypted JSON object passed between parties. Cyber tools use it to verify identity and permissions without querying a central session store.
Adds security auditing for JSON Web Tokens (JWT) in Dynamic Analysis, detecting common flaws like signature vulnerabilities. Adds obsolete JavaScript resource detection in Dynamic Analysis, reporting known-vulnerable libraries (e.g., older jQuery) via signature matching.
2 details in Everything
Veracode Azure DevOps Extension Adds New Scan Summary for Multi-Stage Pipelines
May 19, 2020
· release notes
Veracode Azure DevOps Extension v3.1.0 adds a new Veracode Scan Summary tab for multi-stage pipeline results
Veracode pipeline scan now accepts app and stage metadata via CLI, aiding traceability.
Adds --app_id and --development_stage parameters to the Veracode pipeline scan command
1 detail in Everything
Analytics Scan Frequency Requirements Data
May 13, 2020
· release notes
Veracode Analytics adds visibility into scan frequency requirements including policy mandates and due dates.
Veracode adds Mitigated - Referred to Library Maintainer mitigation type for library findings.
Veracode introduces Team Admin user role to delegate team-level permission management
Adds the Team Admin user role to allow delegated creation, editing, and deletion of users within managed teams. Enables organizations to grant specific teams the ability to manage their own member permissions without full admin rights.
2 details in Everything
Veracode adds prescan-only option and save-draft for Dynamic Analysis on Schedule page.
Adds prescan-only option to verify configuration before submitting the analysis Adds ability to save Dynamic Analysis configuration as a draft for later submission
2 details in Everything
Improved Veracode Static Analysis Support
May 4, 2020
· release notes
Veracode adds static analysis support for Apex 49, Java 14, Play 2.6/2.7 and Python crypto checks, with CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances.
Adds static analysis support for Java applications built on Java 14. Adds static analysis support for Play framework versions 2.6 and 2.7 for Scala. Enables additional security checks for certificate management and cryptography settings in Python application analysis.
3 details in Everything
New Secure Coding Foundation eLearning Courses
Apr 30, 2020
· release notes
Veracode eLearning adds new secure coding foundation courses covering authentication, authorization, data protection, and more.
Updated All Applications page adds customizable columns and improved searching and filtering.
All Applications page now supports customizable columns for the list view.All Applications page includes improved searching and filtering capabilities.
2 details in Everything
Veracode adds new Identity REST APIs REST APIs A convention for building HTTP-based interfaces where resources are addressed by URL and manipulated with standard verbs like GET, POST, and DELETE, giving cyber tools a predictable way to integrate with external services.
Adds support for creating API service accounts via the new Identity REST APIs Adds ability to manage API ID/key credentials through the new Identity REST APIs
2 details in Everything
Improved Veracode Static Analysis Support with Pipeline Scanning
Apr 23, 2020
· release notes
Veracode pipeline scanning adds support for Scala, Kotlin, and Groovy.
Enables Veracode authentication using the API credentials file for pipeline scans.
1 detail in Everything
Veracoda Dynamic Analysis allows scheduling scans up to 90 days in the future.
Adds ability to select a start date up to 90 days in the future for Veracode Dynamic Analysis
1 detail in Everything
Organization Rules for Agent-Based Scans
Apr 6, 2020
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds ability to configure rules for agent-based scans at the organization level in Veracode SCA Enables applying configured rules to all workspaces within an organization to enforce common security standards
2 details in Everything
New Veracode Static Analysis Support
Apr 2, 2020
· release notes
Veracode adds static analysis for AWS Lambda in Java, .NET, Node.js, and Python; iOS 13/Xcode 11.4 support
Adds static analysis support for AWS Lambda functions targeting Java, .NET, Node.js, and Python runtimes. Improves static analysis results quality for iOS 13 applications. Adds support for iOS applications built with Xcode 11.4.
3 details in Everything
└──▷ BREAKING ON UPGRADE
! CWE CWE Common Weakness Enumeration, a catalog of recurring software and hardware weakness types. It describes classes of mistakes, such as injection, rather than individual vulnerability instances. Informational .! Reporting of CWE 404 flaws now includes more specific location data, which may result in additional findings.
Dynamic Analysis User Agent Defaults to Chrome
Mar 31, 2020
· release notes
Dynamic Analysis User Agent now defaults to Chrome if not explicitly configured
Auto-Linking Now Available in Dynamic Analysis
Mar 30, 2020
· release notes
Veracode Dynamic Analysis adds organization-level auto-linking to application profiles.
Enables auto-linking automation at the organization account level in Veracode Dynamic Analysis. Adds the option to automatically create a new application profile for linking future scans.
2 details in Everything
Screenshot Provided for Login Script Errors
Mar 26, 2020
· release notes
Veracode Dynamic Analysis now links to login error screenshots in Prescan Details.
Adds a link to a screenshot of login script errors in the Prescan Details window when authentication fails.
1 detail in Everything
Veracode Azure DevOps Extension Removes Basic Authentication
Mar 24, 2020
· release notes
Veracode Azure DevOps Extension v3.0.0 removes basic auth; requires API ID/key and HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it.
Removes support for username and password authentication in the Veracode Azure DevOps Extension. Requires Veracode API ID and key for authentication in extension configurations.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! The extension no longer accepts username and password credentials; users must migrate to API ID and key authentication.
New Grace Period Expiration Date in Analytics
Mar 19, 2020
· release notes
Veracode Analytics now displays grace period expiration dates for findings.
Analytics display adds the Grace Period Expiration Date to show when a finding's grace period ends Expiring grace periods automatically cause the finding to fail its associated application policy
2 details in Everything
License Risk Details for Agent-Based Scans
Mar 17, 2020
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Adds license risk rating for each open-source license type identified in agent-based scans.
1 detail in Everything
Announcing General Availability of Pipeline Scan for Veracode Static Analysis
Mar 16, 2020
· release notes
Veracato GA release of Pipeline Scan for Static Analysis, a CI-embedded scanning tool.
Announces general availability of Pipeline Scan , a service-enabled integration into CI pipelines for post-commit flaw feedback.
1 detail in Everything
Veracode Dynamic Analysis adds streamlined auto-login for browser-generated and NTLMv2 NTLMv2 A Windows authentication protocol that proves knowledge of a password through a challenge and response. Captured authentication exchanges can be abused in relay attacks when protections are absent.
auto-login is now the default authentication method in Veracode Dynamic Analysis for username/password, browser-generated logins, and NTLMv2A separate basic authentication section allows configuring websites requiring two forms of authentication: auto-login and browser-generated
2 details in Everything
ISM endpoint 20.3.5 adds client-side and 32-bit Java support, proxy gateway-only config, and DSE tunnel diagnostics.
Enables running diagnostics through a DSE tunnel with consolidated diagnostic options
1 detail in Everything
└──▷ BREAKING ON UPGRADE
! The ISM service on Windows now runs under the less privileged LocalService account instead of LocalSystem
Improved Developer Sandbox Scanning and Added Expiration Date
Mar 3, 2020
· release notes
Adds sandbox expiration dates and limits simultaneous scans to ten.
Limits simultaneous developer sandbox scans to ten per application, requiring completion of one before starting additional ones Shows all sandboxes with running scans in the application profile's sandbox list Adds expiration dates to all sandboxes, after which scanning is disabled and the platform automatically removes the sandbox seven days later
3 details in Everything
Executive Summary in Customizable Report PDF Includes Informational Findings
Mar 3, 2020
· release notes
Customizable Report PDF executive summary now includes informational findings.
Email Notifications for eLearning Curriculum Due Date Changes
Mar 3, 2020
· release notes
Veracode eLearning admin email notifications for curriculum due date changes
eLearning administrators can now send emails to notify students and their managers when the due date for an assigned curriculum changes.
1 detail in Everything
Veracode Static for Eclipse Supports Eclipse 2019-09
Jan 31, 2020
· release notes
Veracode Static for Eclipse 3.4.0 adds Eclipse 2019-09 and JRE support; requires API ID/key auth.
Adds support for Java Runtime Environment (JRE) versions 11 and 13 Requires HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! Removes support for basic authentication (username and password); users must now use Veracode API ID and key authentication.
Update to Integrated SCA Upload and Scan
Jan 29, 2020
· release notes
Veracigo Integrated SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Enables Integrated SCA scans via the upload and scan method for users without a Static Analysis subscription Extends Integrated SCA support to include the upload and scan workflow
2 details in Everything
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Sandbox policy promotion now deletes associated scans; new 25-sandbox default limit per application.
Sets the default maximum number of sandboxes per application to 25
1 detail in Everything
└──▷ BREAKING ON UPGRADE
! Promoting a sandbox to policy now automatically deletes that sandbox and all of its scans.
Automated Emails for eLearning Curriculum Updates
Jan 28, 2020
· release notes
Veracode eLearning administrators can now enable automated email alerts for curriculum assignments.
Veracode Static for IntelliJ Supports IntelliJ IDEA 2019.3
Jan 24, 2020
· release notes
Veracode Static for IntelliJ 3.0.0 introduces API ID/key auth and JRE support
Adds API ID and key authentication as the required method for connecting to Veracode services Adds support for Java Runtime Environment (JRE) versions 11 and 13 Replaces the legacy Veracode IntelliJ Plugin with version 3.0.0
3 details in Everything
└──▷ BREAKING ON UPGRADE
! Removes support for basic authentication (username and password)! Requires custom integration scripts to include HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it.
Updated Veracode Integration for Jira
Jan 23, 2020
· release notes
Veracode Jira Integration v3.22.0 drops basic auth, adds HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it.
veracode_api_id and veracode_api_key must replace username/password for authenticationCustom integration scripts must implement HMAC signing to communicate with Veracode
2 details in Everything
└──▷ BREAKING ON UPGRADE
! Basic authentication is removed; username and password are no longer accepted for the Veracode Integration for Jira.
Veracode Static for Visual Studio Supports Visual Studio 2019
Jan 17, 2020
· release notes
Veracode Static for Visual Studio v4.0.0.1 adds VS 2019 support and requires API credentials file.
Replaces the previous Veracode for Visual Studio Extension . Requires configuration of an API credentials file to provide API ID and key.
2 details in Everything
└──▷ BREAKING ON UPGRADE
! The Veracode for Visual Studio Extension is replaced by Veracode Static for Visual Studio .! In Visual Studio 2015 and 2017, the top-level menu name changes to Veracode Static .! In Visual Studio 2019, the Veracode Static menu is now located under Extensions .! An API credentials file must be configured to use the tool.
Get Teams List with the SCA Agent REST API
Jan 15, 2020
· release notes
Veracode SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. REST API REST API A web API design style where clients interact with resources over HTTP using standard methods like GET, POST, and DELETE, giving cyber tools a predictable, language-agnostic way to integrate with external services.
Adds the GET /rest/scanning/v1/teams endpoint to list all teams in an organization.
1 detail in Everything
SCA Findings Dashboard Available in Analytics
Jan 13, 2020
· release notes
Veracode Analytics gains a new SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Change to Failed Verification Status
Jan 8, 2020
· release notes
Veracode Dynamic Analysis now distinguishes All Verifications Failed from Completed - Partial Results Available for failed URL scans.
Updates the status shown when a single URL scan fails verification to Verification Failed , with the overall Dynamic Analysis status set to All Verifications Failed . Updates the status shown when multiple URL scans in an analysis have at least one failure, changing the analysis status to Completed - Partial Results Available while keeping individual failed scans as Verification Failed .
2 details in Everything
Updated Veracode Integration for Jira Cloud
Jan 8, 2020
· release notes
Veracode Jira Integration v3.2.0 adds severity mapping, Description overwrite, SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself. HMAC HMAC A keyed hash that proves a message came from someone holding a shared secret and was not altered. Webhooks and API request signing commonly use it.
Adds a new Veracode Integration Severity Mappings page in the Jira Cloud interface for mapping Veracode Platform severities to Jira priorities Adds Description (overwrite) option on the Veracode Integration Field Mapping page to control overwriting or erasing Jira Description fields during import Adds an option for mapping Veracode SCA component paths on the Veracode Integration Field Mapping page Removes basic authentication support, requiring Veracode API ID and key with HMAC signing for all integration scripts
4 details in Everything
└──▷ BREAKING ON UPGRADE
! Basic authentication is removed; you must now use Veracode API ID and key authentication! Custom integration scripts must include HMAC signing
Veracode Dynamic Analysis adds Auto-Publish to instantly export specific vulnerability findings
Enables Auto-Publish in Veracode Dynamic Analysis to automatically publish some findings for quicker results. Automatically publishes all findings immediately after analysis if every vulnerability meets auto-publication criteria. Publishes all findings together within 24 hours of manual review completion when any vulnerability requires engineer review.
3 details in Everything
SCA Findings Available in Veracode Analytics
Jan 2, 2020
· release notes
SCA SCA Software composition analysis, identifying third-party dependencies and checking them for known vulnerabilities and license issues. It covers software a team uses rather than writes itself.
Displays Software Composition Analysis (SCA) vulnerability details in the Findings Status & History dashboard for users with an SCA subscription Displays Software Composition Analysis (SCA) vulnerability details in the Resolution and Mitigation Details dashboard for users with an SCA subscription
2 details in Everything
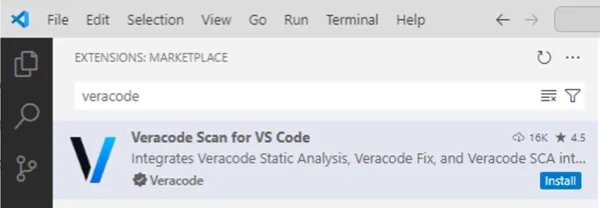 Integration updates (2026-10-30) · Oct 2026
· source
· release history
 Choose a badge style and copy the code →