Auth0
Multi-Factor Authentication: Exponential Backoff for Phone MFA SMS Delivery (2026-10-30) commercialThe section your link pointed to isn't on Auth0's page any more, so we've brought you to the top.
module "b2b_saas" {
  source  = "auth0/modules/auth0//modules/b2b-saas-starter"
  version = "~> 1.0"

  app_name      = "Acme"
  app_callbacks = ["https://app.acme.com/callback"]
  app_logout_urls = ["https://app.acme.com"]
  app_origins   = ["https://app.acme.com"]

  api_name       = "Acme API"
  api_identifier = "https://api.acme.com"

  roles = ["admin", "member"]
  permissions = {
    admin  = ["read:projects", "write:projects", "manage:members"]
    member = ["read:projects"]
  }
}
module "b2b_saas" {
  source  = "auth0/modules/auth0//modules/b2b-saas-starter"
  version = "~> 1.0"

  app_name      = "Acme"
  app_callbacks = ["https://app.acme.com/callback"]
  app_logout_urls = ["https://app.acme.com"]
  app_origins   = ["https://app.acme.com"]
  api_name       = "Acme API"
  api_identifier = "https://api.acme.com"

  organizations = [
    {
      name         = "globex-corp"
      display_name = "Globex Corp"
      connection = {
        type             = "samlp"
        domain_aliases   = ["globex.com"]
        sign_in_endpoint = "https://idp.globex.com/sso"
        signing_cert     = file("globex-cert.pem")
      }
    }
  ]
}
module "admin_portal" {
  source  = "auth0/modules/auth0//modules/b2b-saas-starter"
  version = "~> 1.0"

  app_name        = "Acme Admin"
  app_callbacks   = ["https://admin.acme.com/callback"]
  app_logout_urls = ["https://admin.acme.com"]
  app_origins     = ["https://admin.acme.com"]

  manage_tenant           = false
  manage_attack_protection = false
  manage_mfa              = false
}
auth0 commands --flat --detailed
auth0 apps create --schema
auth0 apps create --agent-mode --data '{"name":"billing-app","app_type":"spa"}'
export AUTH0_CLI_AUTH_MODE=env
export AUTH0_DOMAIN=<your-auth0-domain>
export AUTH0_API_TOKEN=<management-api-token>
auth0 apps list --agent-mode --json-compact
auth0 logs list --agent-mode --query '{"per_page":5}'
// shared/build.gradle.kts
kotlin {
  sourceSets {
    commonMain.dependencies {
      implementation("com.auth0.kmp:auth0:1.0.0-beta.1")
    }
  }
}
import com.auth0.kmp.Auth0
import com.auth0.kmp.core.Auth0Account

val account = Auth0Account(
  clientId = "<YOUR_CLIENT_ID>",
  domain = "<YOUR_DOMAIN>",
  useDPoP = true
)
val auth0 = Auth0(account)
import com.auth0.kmp.core.result.Result

val manager = auth0.credentials()
when (val result = manager.getCredentials()) {
  is Result.Success -> {
    val accessToken = result.data.accessToken
    // attach accessToken to downstream API requests
  }
  is Result.Failure -> {
    // result.error is a CredentialsManagerError — prompt re-login
  }
}
npm install @auth0/auth0-tanstack-start-react
AUTH0_DOMAIN=YOUR_AUTH0_APP_DOMAIN
AUTH0_CLIENT_ID=YOUR_AUTH0_APP_CLIENT_ID
AUTH0_CLIENT_SECRET=YOUR_AUTH0_APP_CLIENT_SECRET
AUTH0_SECRET=$(openssl rand -hex 32)
APP_BASE_URL=http://localhost:3000
import { createFileRoute } from '@tanstack/react-router';
import { requireAuth, useUser } from '@auth0/auth0-tanstack-start-react/client';

export const Route = createFileRoute('/dashboard')({
  beforeLoad: requireAuth({ returnTo: '/dashboard' }),
  component: Dashboard,
});

function Dashboard() {
  const user = useUser();
  return <h1>Welcome, {user?.name}!</h1>;
}
exports.onExecutePreUserRegistration = async (event, api) => {
  const crypto = require('crypto');
  api.user.setUserId(crypto.randomUUID());
};
exports.onExecutePreUserRegistration = async (event, api) => {
  const crypto = require('crypto');
  api.user.setUserId(crypto.randomUUID());
};
exports.onExecutePreUserRegistration = async (event, api) => {
  const crypto = require('crypto');
  api.user.setUserId(crypto.randomUUID());
};
curl -X PATCH 'https://<tenant>.auth0.com/api/v2/organizations/<org_id>/connections/<connection_id>' \
  -H 'Authorization: Bearer <mgmt_api_token>' \
  -H 'Content-Type: application/json' \
  -d '{"organization_member_access_level": "limited"}'
exports.onExecutePreUserRegistration = async (event, api) => {
  const crypto = require('crypto');
  api.user.setUserId(crypto.randomUUID());
};
match_all: true
npx skills add auth0/agent-skills
curl -X GET 'https://{yourDomain}/me/v1/authentication-methods' \
  -H 'Authorization: Bearer <access_token>'
curl -X POST 'https://{yourDomain}/me/v1/authentication-methods/{id}/verify' \
  -H 'Authorization: Bearer <access_token>'
curl -X POST https://<tenant>.auth0.com/api/v2/network-acls \
  -H 'Authorization: Bearer <mgmt_api_token>' \
  -H 'Content-Type: application/json' \
  -d '{
    "description": "Block TOR and low-reputation IPs",
    "active": true,
    "priority": 1,
    "rule": {
      "action": { "block": true },
      "match": {
        "auth0_managed": ["auth0.tor", "auth0.low_reputation"]
      },
      "scope": "authentication"
    }
  }'
curl -X POST https://<tenant>.auth0.com/api/v2/network-acls \
  -H 'Authorization: Bearer <mgmt_api_token>' \
  -H 'Content-Type: application/json' \
  -d '{
    "description": "Block TOR exit nodes",
    "active": true,
    "priority": 2,
    "rule": {
      "action": { "block": true },
      "match": { "auth0_managed": ["auth0.tor"] },
      "scope": "authentication"
    }
  }'
auth0 api post metric-streams \
  --data '{
    "name": "datadog-production",
    "subscriptions": [{ "metric_type": "auth0.api_request.count" }],
    "destination": {
      "type": "datadog",
      "configuration": {
        "api_key": "YOUR_DATADOG_API_KEY",
        "site": "app.datadoghq.com"
      }
    }
  }'
auth0 api post metric-streams \
  --data '{
    "name": "newrelic-production",
    "subscriptions": [{ "metric_type": "metrics_bridge.api_request" }],
    "destination": {
      "type": "otlp",
      "configuration": {
        "endpoint": "https://otlp.nr-data.net",
        "protocol": "http",
        "auth_type": "api_key",
        "api_key": "YOUR_INGEST_LICENSE_KEY",
        "auth_header_name": "api-key"
      }
    }
  }'
auth0 api patch /api/v2/metric-streams/YOUR_STREAM_ID \
  --data '{"status":"disabled"}'

# Later, re-enable:
auth0 api patch /api/v2/metric-streams/YOUR_STREAM_ID \
  --data '{"status":"enabled"}'
auth0 api post metric-streams \
  --data '{
    "name": "datadog-production",
    "subscriptions": [{ "metric_type": "auth0.api_request.count" }],
    "destination": {
      "type": "datadog",
      "configuration": {
        "api_key": "YOUR_DATADOG_API_KEY",
        "site": "app.datadoghq.com"
      }
    }
  }'
auth0 api post metric-streams \
  --data '{
    "name": "newrelic-production",
    "subscriptions": [{ "metric_type": "metrics_bridge.api_request" }],
    "destination": {
      "type": "otlp",
      "configuration": {
        "endpoint": "https://otlp.nr-data.net",
        "protocol": "http",
        "auth_type": "api_key",
        "api_key": "YOUR_INGEST_LICENSE_KEY",
        "auth_header_name": "api-key"
      }
    }
  }'
auth0 api patch /api/v2/metric-streams/YOUR_STREAM_ID \
  --data '{"status":"disabled"}'

# Later, re-enable:
auth0 api patch /api/v2/metric-streams/YOUR_STREAM_ID \
  --data '{"status":"enabled"}'
curl --request PATCH \
  --url 'https://<tenant>.auth0.com/api/v2/connections/<connection_id>' \
  --header 'Authorization: Bearer <mgmt_api_token>' \
  --header 'Content-Type: application/json' \
  --data '{"is_domain_connection": true}'
// Post-Login Action
exports.onExecutePostLogin = async (event, api) => {
  const sessionExpiry = event.session?.expiry;
  if (sessionExpiry) {
    api.idToken.setCustomClaim('session_expiry', sessionExpiry);
  }
};
curl -X PATCH https://<your-tenant>.auth0.com/api/v2/connections/<connection_id> \
  -H 'Authorization: Bearer <mgmt_api_token>' \
  -H 'Content-Type: application/json' \
  -d '{"options": {"session_expiry": true}}'
// Post-Login Action
exports.onExecutePostLogin = async (event, api) => {
  api.refreshToken.setMetadata('deviceName', event.request.user_agent);
  api.refreshToken.setMetadata('loginRegion', event.request.geoip?.countryCode);
  api.refreshToken.setMetadata('orgContext', event.organization?.id);
};
curl -X GET "https://<your-domain>/api/v2/refresh-tokens/<id>" \
  -H "Authorization: Bearer <mgmt_api_token>"
curl -X PATCH "https://<your-domain>/api/v2/refresh-tokens/<id>" \
  -H "Authorization: Bearer <mgmt_api_token>" \
  -H "Content-Type: application/json" \
  -d '{"metadata": {"stepUpCompleted": "true"}}'
Summary
Auth0 is a commercial identity-access platform, run as SaaSSaaSSoftware delivered over the internet and run on the provider's infrastructure, so the buyer pays a subscription instead of installing or operating anything locally., that handles authentication and authorization for applications so development teams don't build login, session management, and access control themselves. It's aimed at application developers and platform teams who need to add sign-in, federated identity, and role-based permissions without owning the underlying protocol work — SDKs cover React, Angular, Next.js, iOS, Android, Java, .NET, and Python. Recent work spans enterprise session control, such as tying Auth0 session expiry to an upstream IdPIdPA service that authenticates users and supplies identity information to other applications. It is the sign-in authority behind many single sign-on systems.'s own expiry claim, and organization-level features like per-org third-party app access, Google Workspace group sync into RBACRBACRole-based access control, where permissions are assigned to roles such as reader or administrator and users receive those roles. It makes access easier to manage than individual permission lists. roles, and SCIMSCIMA standard for creating, updating and removing user accounts and groups across applications. It helps an identity provider keep access in sync when people join, change roles or leave.-based user provisioning to downstream apps.
How Auth0 helps
Which third-party applications can pull user identity from a given organization, and which ones are locked out until an admin opts in?
checks the per-organization access setting, which defaults to blocked for every existing organization, and shows only the orgs where an admin has explicitly enabled a given third-party app
How do I get new and changed users into a downstream SCIM app without standing up my own sync service?
translates user.created, user.updated, and user.deleted lifecycle events into SCIM 2.0 REST calls through an Action template, with retry handling built in for transient failures
Which refresh tokens were issued from an unusual device or region, or carry elevated privileges after step-up auth?
stores up to 25 custom key-value pairs per refresh token at login and exposes them through the Management API, so a token's device, region, or elevation state can be looked up or patched without re-querying the IdP
Do members of a Google Workspace group already have the right tenant permissions, or do I have to assign them by hand?
syncs Workspace groups and maps them directly to Auth0 RBAC roles, so group members inherit the mapped permissions automatically at their next login
Languages
Features
Built from Auth0's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
What Auth0 offers you
- REST API9
- Web management console5
- Role-based access control4
- Administrative audit log3
- Client SDKs2
- Command-line interface2
- Multi-factor authentication2
- Multi-tenant management2
- SCIM provisioning API2
- JSON data export1
- Natural-language query1
- OIDC SSO1
- Outbound webhooks (the product notifies you)1
- SAML SSO1
- Scripting API1
- SIEM forwarding1
- Single sign-on1
No capabilities match.
Single sign-on 1 feature Identity and access since 2026
Self-Service Enterprise Configuration third-party access delegation shipped Allows the third-party application access decision to be delegated to the customer admin during Self-Service Enterprise Configuration SSO ticket setup, surfacing a new wizard step instead of requiring the setting at ticket creation time.
Shared capability: Single sign-on
release
- Layer enterprise SSO and self-service onboarding/setup flows on top of federated connections for B2B customers. Enterprise Connect - Beta (2026-07-30) · Jul 2026 · source · release history
-
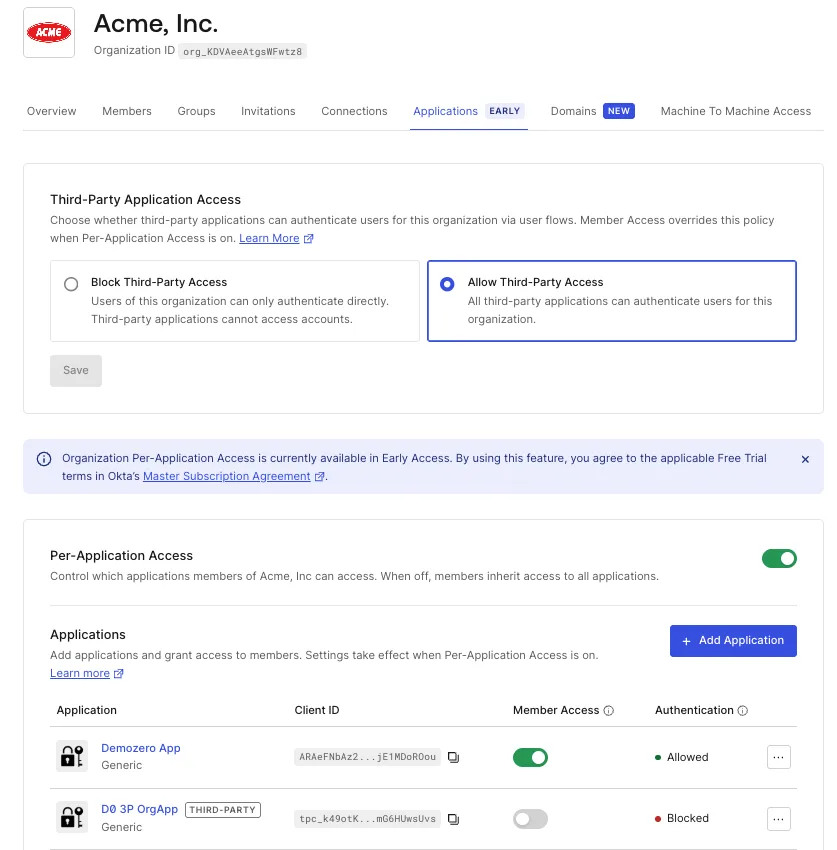
Self-Service Enterprise Configuration tickets can now delegate third-party application access decisions to the customer admin, surfacing a new wizard step during SSO setup rather than requiring the setting at ticket creation time.
 changelog · Jul 2026
· source
· release history
- Enables delegation of the third-party application access decision to customer admins during Self-Service Enterprise Configuration ticket setup, surfacing a new wizard step where they can allow or skip third-party SSO access. Self-Service Enterprise Configuration: Customer admins can now configure third-party application access during SSO setup (2026-07-22) · Jul 2026 · source · release history
docs
- July 22, 2026 Self-Service Enterprise Configuration: Customer admins can now configure third-party application access during SSO setup When generating a Self-Service Enterprise Configuration ticket, you can now delegate the third-party application access decision to your customer's customer admin — rather than setting… changelog · Jul 2026 · source
example
-
When creating a Self-Service Enterprise Configuration ticket, delegate the third-party access decision to the customer admin instead of setting it yourself — useful when you want customers to self-govern whether third-party apps can use their SSO connection.
In the Auth0 console, go to Authentication > Enterprise > Self-Service Enterprise Configuration, create or edit a ticket, and enable third-party access delegation on the ticket instead of setting…Self-Service Enterprise Configuration: Customer admins can now configure third-party application access during SSO setup (2026-07-22) · Jul 2026 · source
SAML SSO 1 feature Identity and access since 2026
Enterprise Connect shipped Federates existing SAML or OIDC authorization servers (including Okta) into Auth0 as a B2B identity layer, layering enterprise SSO, SCIM user provisioning, self-service onboarding, Actions-based claim enrichment, and connection lifecycle events on top of those federated connections.
Shared capability: SAML SSO
Also counts toward: SCIM provisioning API, Single sign-on, OIDC SSO, SAML SSO
release
-
Adds an
organizationsinput that creates Auth0 Organizations with per-customer enterprise SSO connections, supportingtype = "samlp"(SAML) andtype = "oidc"(OIDC),domain_aliases,sign_in_endpoint, andsigning_cert. announced · Oct 2026 · source · release history -
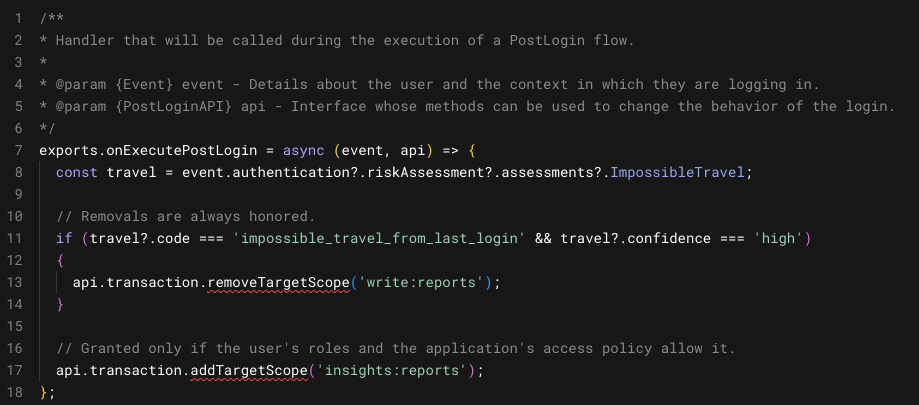
Picks up changes to a client's metadata and public signing keys automatically, without manual syncing.
 CIMD with Dynamic Registration in Early Access (2026-10-22) · Oct 2026
· source
· release history
-
Introduces Enterprise Connect (Beta), letting you federate existing SAML or OIDC authorization servers (including Okta) into Auth0 and layer on enterprise SSO, SCIM user provisioning, and self-service B2B onboarding with Actions-based claim enrichment and connection lifecycle events.
changelog · Aug 2026
· source
· release history
-
Subscribe to connection lifecycle events (
connection.created,connection.updated,connection.deleted) to keep local domain maps in sync as customers onboard. Enterprise Connect - Beta (2026-07-30) · Jul 2026 · source · release history - Inject user profile claims into ID tokens using Actions code during federated authentication. Enterprise Connect - Beta (2026-07-30) · Jul 2026 · source · release history
- Federate existing SAML or OIDC authorization servers (including Okta) to Auth0 as a modular B2B identity layer. Enterprise Connect - Beta (2026-07-30) · Jul 2026 · source · release history
OIDC SSO 1 feature Identity and access since 2026
Federated session expiry enforcement shipped Terminates Auth0 sessions when an upstream IdP session expires by honouring the IPSIE SL1 session_expiry claim on Okta and OIDC Enterprise connections, enforcing the minimum of IdP, tenant, and Action-set expiry values, and optionally propagating the final expiry to downstream apps via a custom ID token claim.
Shared capability: OIDC SSO
release 7 total
-
Enables automatic session termination in the application when the external enterprise IdP ends its session, keeping app state synchronized with the directory.
 B2B Connect - Enterprise in Early Access! (2026-09-16) · Sep 2026
· source
· release history
- Automatically terminates active application sessions when the enterprise IdP ends the corresponding session, keeping app and IdP session state in sync. B2B Connect - Enterprise in Early Access! (2026-09-16) · Sep 2026 · source · release history
- Automatically terminates Auth0 sessions when a federated user's upstream IdP session expires, eliminating stale federated sessions and residual access. IPSIE session_expiry Claim Support for Okta and OIDC Enterprise Connections (2026-07-08) · Jul 2026 · source · release history
-
Enables propagation of the final
session_expiryvalue to downstream applications via a Post-Login Action that injects it as a custom claim in the Auth0-issued ID token. IPSIE session_expiry Claim Support for Okta and OIDC Enterprise Connections (2026-07-08) · Jul 2026 · source · release history -
Supports the IPSIE SL1
session_expiryclaim for Okta and OIDC Enterprise connections, using the IdP-provided expiry as a hard ceiling on Auth0 session lifetime. IPSIE session_expiry Claim Support for Okta and OIDC Enterprise Connections (2026-07-08) · Jul 2026 · source · release history -
Enforces session expiry as the minimum of three values: the IdP
session_expiryclaim, the tenant's absolute session expiration, and any expiry set via Actions. IPSIE session_expiry Claim Support for Okta and OIDC Enterprise Connections (2026-07-08) · Jul 2026 · source · release history
example
-
Enable session_expiry enforcement on an existing OIDC Enterprise connection via the Management API.
curl -X PATCH https://<your-tenant>.auth0.com/api/v2/connections/<connection_id> \ -H 'Authorization: Bearer <mgmt_api_token>' \ -H 'Content-Type: application/json' \ -d '{"options":…IPSIE session_expiry Claim Support for Okta and OIDC Enterprise Connections (2026-07-08) · Jul 2026 · source -
Enable session_expiry support on an Okta/OIDC Enterprise connection through the Auth0 Dashboard.
In the Auth0 Dashboard, go to Authentication > Enterprise, select your Okta or OIDC connection, open its settings, and enable the Session Expiry option.IPSIE session_expiry Claim Support for Okta and OIDC Enterprise Connections (2026-07-08) · Jul 2026 · source -
Propagate the enforced session expiry to downstream apps so they can respect the IdP-driven session ceiling end-to-end.
// Post-Login Action exports.onExecutePostLogin = async (event, api) => { const sessionExpiry = event.session?.expiry; if (sessionExpiry) { api.idToken.setCustomClaim('session_expiry',…IPSIE session_expiry Claim Support for Okta and OIDC Enterprise Connections (2026-07-08) · Jul 2026 · source
Role-based access control 1 feature Identity and access since 2026
Google Workspace Directory Sync for Groups shipped Synchronises Google Workspace groups into Auth0, supporting automated full or partial group sync and native assignment of synced groups to tenant-level and organization-specific RBAC roles.
Shared capability: Role-based access control
Also counts toward: Role-based access control
release 9 total
-
Self-Service Selective Group Sync lets enterprise IT admins independently configure Google Workspace Directory Sync and choose which groups to sync via the self-service assistant flow.
changelog · Aug 2026
· source
· release history
- New paginated, searchable table in the Auth0 Management Dashboard lets tenant admins browse, filter, and search synced Google Workspace groups. changelog · Aug 2026 · source · release history
- Google Workspace Inbound Directory Sync for Groups and Group Membership is now Generally Available for all Auth0 customers. changelog · Aug 2026 · source · release history
- Adds paginated, searchable, filterable table in the Auth0 Management Dashboard for browsing and selecting Google Workspace groups to sync. Google Workspace Directory Sync for Groups - Now in General Availability! (2026-08-06) · Aug 2026 · source · release history
- Enables self-service selective Google Workspace Directory Sync for Groups via the Self-Service assistant flow, letting enterprise IT admins choose all or a subset of groups to synchronize. Google Workspace Directory Sync for Groups - Now in General Availability! (2026-08-06) · Aug 2026 · source · release history
- Adds support for Group and Group Membership synchronization in Google Workspace Inbound Directory Sync (GA) Google Workspace Directory Sync for Groups - Now in General Availability! (2026-08-06) · Aug 2026 · source · release history
example
-
Enable IT teams to self-configure group syncing via the management console
In the Auth0 Management Dashboard, navigate to Enterprise Connections and use the Self-Service assistant flow to sync Google Workspace groups.Google Workspace Directory Sync for Groups - Now in General Availability! (2026-08-06) · Aug 2026 · source -
Assign a synced Google Workspace group to an Auth0 RBAC role so members automatically receive the correct permissions when they log in.
In the Auth0 Dashboard, go to Authentication > Enterprise > Google Workspace connection > Synchronization, configure your group synchronization preferences, then navigate to User Management > Roles >…Google Workspace Directory Sync for Groups - Early Access Updates (2026-06-17) · Jun 2026 · source
MCP server 1 feature Interfaces and integrations since 2026
External Agent Identifier Association shipped Associates existing external agent identifiers (from an own registry, MCP server, or elsewhere) with an Auth0 client, avoiding re-provisioning of already-built agents.
Shared capability: MCP server
release
- Supports associating existing external agent identifiers (from your own registry, an MCP server, or elsewhere) with an Auth0 client, avoiding re-provisioning of already-built agents. Agents as Principal now in Early Access! (2026-07-30) · Jul 2026 · source · release history
Other / not yet classified 51 features Features we have not matched to a capability yet. A suggested match is marked.
Session Delegation via Custom Token Exchange shipped Allows one party (e.g. a support agent) to obtain a Session Transfer Token that delegates into a target user's session via the standard `/authorize` endpoint, preserving both the user's `sub` claim and the RFC 8693 `act` claim for the acting party, with dedicated tenant log events for compliance and traceability.
release 18 total
-
Enables Session Delegation through Custom Token Exchange, allowing a service, AI agent, or support agent to establish a web session on behalf of a user.
changelog · Aug 2026
· source
· release history
-
Built on Auth0 Token Vault using the ID-JAG (Identity Assertion Authorization Grant) protocol; currently supported on OIDC and Okta Workforce connections.
 Cross-App Access Requesting App now in Early Access (2026-08-31) · Aug 2026
· source
· release history
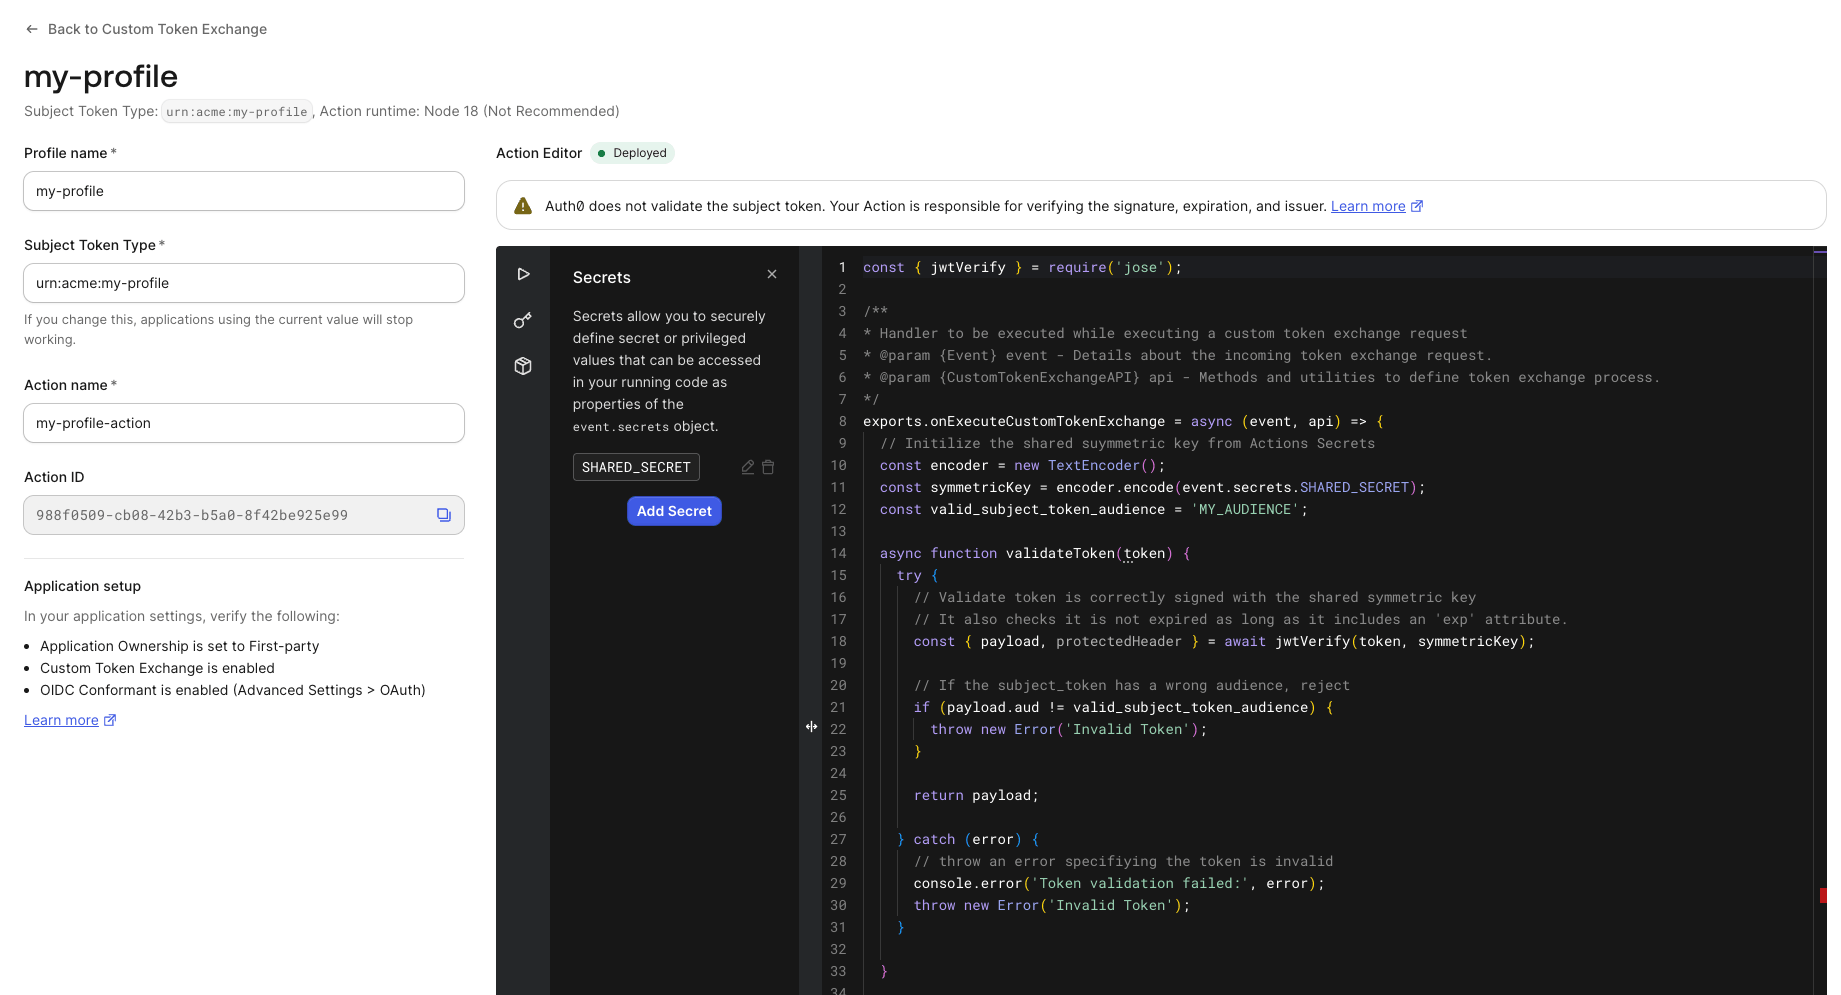
- Custom Token Exchange is now Generally Available for Enterprise, B2B Professional, and B2C Professional customers and during Trial periods — lets applications exchange an existing Auth0 or external-IdP token for Auth0 access, ID, and refresh tokens via custom Action logic. changelog · Aug 2026 · source · release history
- Adds shared transaction context between Custom Token Exchange Actions and Post-Login Actions via transaction metadata, enabling token customization based on subject or actor token information. changelog · Aug 2026 · source · release history
- Introduces Custom Token Exchange (GA), allowing applications to exchange an existing token — issued by Auth0 or an external identity provider — for Auth0 access, ID, and refresh tokens, validated by a Custom Token Exchange Action. Custom Token Exchange is now Generally Available (2026-08-28) · Aug 2026 · source · release history
- Adds General Availability for Custom Token Exchange to Enterprise, B2B Professional, and B2C Professional tiers, enabling token exchange via custom Action logic. Custom Token Exchange is now Generally Available (2026-08-28) · Aug 2026 · source · release history
docs
-
to the audience of the incoming token (i.e.
https://incoming-token-api.example.com), not the downstream API. Auth0 uses the resource server identifier to validate the incoming token before performing the OBO token exchange. seen Sep 2026 · source - August 28, 2026 Version 202634 We are excited to announce that Custom Token Exchange is now Generally Available. This feature is available to all Enterprise, B2B Professional, and B2C Professional customers, as well as part of the Trial period for free tenants. changelog · Aug 2026 · source
- August 7, 2026 202632 Custom Token Exchange - Session Delegation is now available in Open Early Access Auth0 now supports Session Delegation via Custom Token Exchange . This release is available to all Enterprise, B2B Professional, and B2C Professional customers. changelog · Aug 2026 · source
- The delegation chain is limited to five nested levels. Because the exchange appends the current client as one more level, the OBO token exchange will fail if the subject token already has four nested seen Aug 2026 · source
example
-
Create and configure a Custom Token Exchange Profile and its Action directly from the Dashboard to support AI-agent delegated authorization.
1. In the Auth0 Dashboard, go to Actions > Custom Token Exchange Profiles. 2. Click 'Create Profile' and specify the subject token type (Auth0 or external IdP). 3.changelog · Aug 2026 · source -
Pass context from the exchange action into the post-login hook to customize the resulting token.
// In your Custom Token Exchange Action context.transactionMetadata = { customKey: 'value' }; // In your Post-Login Action const value = context.transactionMetadata.customKey;Custom Token Exchange is now Generally Available (2026-08-28) · Aug 2026 · source -
Manage new CTE profiles visually instead of relying solely on API/CLI for setup.
In the Auth0 Dashboard, go to Actions > Library and create a 'Custom Token Exchange Profile'.Custom Token Exchange is now Generally Available (2026-08-28) · Aug 2026 · source
Curated Blocklists for Tenant ACLs shipped Integrates dynamically updated Auth0 Threat Intel categories (low reputation, TOR, proxy, VPN, iCloud Relay) into Network ACL rules via an `auth0_managed` matcher block, so Attack Protection customers can delegate IP risk management to Auth0 instead of maintaining manual IP/ASN lists.
release 11 total
-
Adds Unblock Behavior setting to Brute-Force Protection with Automatic (default) and Manual modes — Manual mode presents a confirmation page so headless email scanners (e.g.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Microsoft 365 Defender) cannot silently consume the recovery link before the user opens it.
Configurable Unblock Mode for Brute Force Protection (2026-10-22) · Oct 2026
· source
· release history
- Adds Instant Status Toggles to enable or disable individual Tenant ACL rules in a single click while Auth0 handles the underlying API calls. Tenant ACL Dashboard UX (2026-10-12) · Oct 2026 · source · release history
- Adds a Visual Rule Sequencing canvas to reorder Tenant ACL policy priorities and inspect exact rule execution order. Tenant ACL Dashboard UX (2026-10-12) · Oct 2026 · source · release history
- Adds a Guided Rule Builder under Security > Access Control with step-by-step prompts for scope, entity, and action selection to construct Tenant ACL policies without syntax errors.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Tenant ACL Dashboard UX (2026-10-12) · Oct 2026 · source · release history
-
Adds
match_all: trueattribute to Tenant Access Control List (ACL) rules, enabling a Deny All rule that rejects all incoming traffic across the full tenant scope without requiring specific signal matching (IP, geolocation, etc.).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
changelog · Sep 2026
· source
· release history
-
Adds
match_all: trueconfig key in Tenant ACL rules to reject all traffic regardless of IP or geolocation signals
New Deny All Rule for Tenant ACL (2026-09-08) · Sep 2026
· source
· release history
docs
- September 8, 2026 You can now configure a Deny All rule within your Tenant Access Control List (ACL) to reject all incoming traffic to your assigned scope. changelog · Sep 2026 · source
example
-
Enable Manual unblock mode so Microsoft 365 Defender and similar link-scanning gateways cannot auto-consume brute-force recovery links.
1. Go to Auth0 Dashboard > Security > Attack Protection > Brute-Force Protection. 2. Scroll to 'Unblock Behavior'. 3. Select 'Manual'. 4. Click 'Save'.Configurable Unblock Mode for Brute Force Protection (2026-10-22) · Oct 2026 · source -
Create and activate a new Tenant ACL rule without writing raw policy syntax — useful for teams who need to restrict tenant access quickly during an incident.
1. Navigate to Security > Access Control in the Auth0 dashboard. 2. Click 'New Rule' to open the Guided Rule Builder. 3. Step through the scope, entity, and action prompts and save. 4.Tenant ACL Dashboard UX (2026-10-12) · Oct 2026 · source -
Adjust enforcement order when a newly added deny rule must take precedence over existing allow rules — prevents unintended access due to rule sequencing.
1. Navigate to Security > Access Control in the Auth0 dashboard. 2. Open the Visual Rule Sequencing canvas. 3. Drag the deny rule above the relevant allow rules to set correct execution order. 4.Tenant ACL Dashboard UX (2026-10-12) · Oct 2026 · source -
Block all traffic from active TOR exit nodes and low-reputation IPs at the tenant level using curated Auth0 Threat Intel lists.
curl -X POST https://<tenant>.auth0.com/api/v2/network-acls \ -H 'Authorization: Bearer <mgmt_api_token>' \ -H 'Content-Type: application/json' \ -d '{ "description": "Block TOR and low-reputation…changelog · Aug 2026 · source -
Block all TOR exit node traffic at the authentication scope to prevent anonymous abuse via TOR.
curl -X POST https://<tenant>.auth0.com/api/v2/network-acls \ -H 'Authorization: Bearer <mgmt_api_token>' \ -H 'Content-Type: application/json' \ -d '{ "description": "Block TOR exit nodes",…Curated Blocklists in Tenant Access Control Lists is Now GA! (2026-07-30) · Jul 2026 · source
Anonymous Sessions shipped Creates and manages stateless sessions for unauthenticated users, with configurable session length per tenant, application, and API, cross-device activity preservation on login, and session linking to authenticated profiles via Actions.
Also counts toward: REST API
release 12 total
-
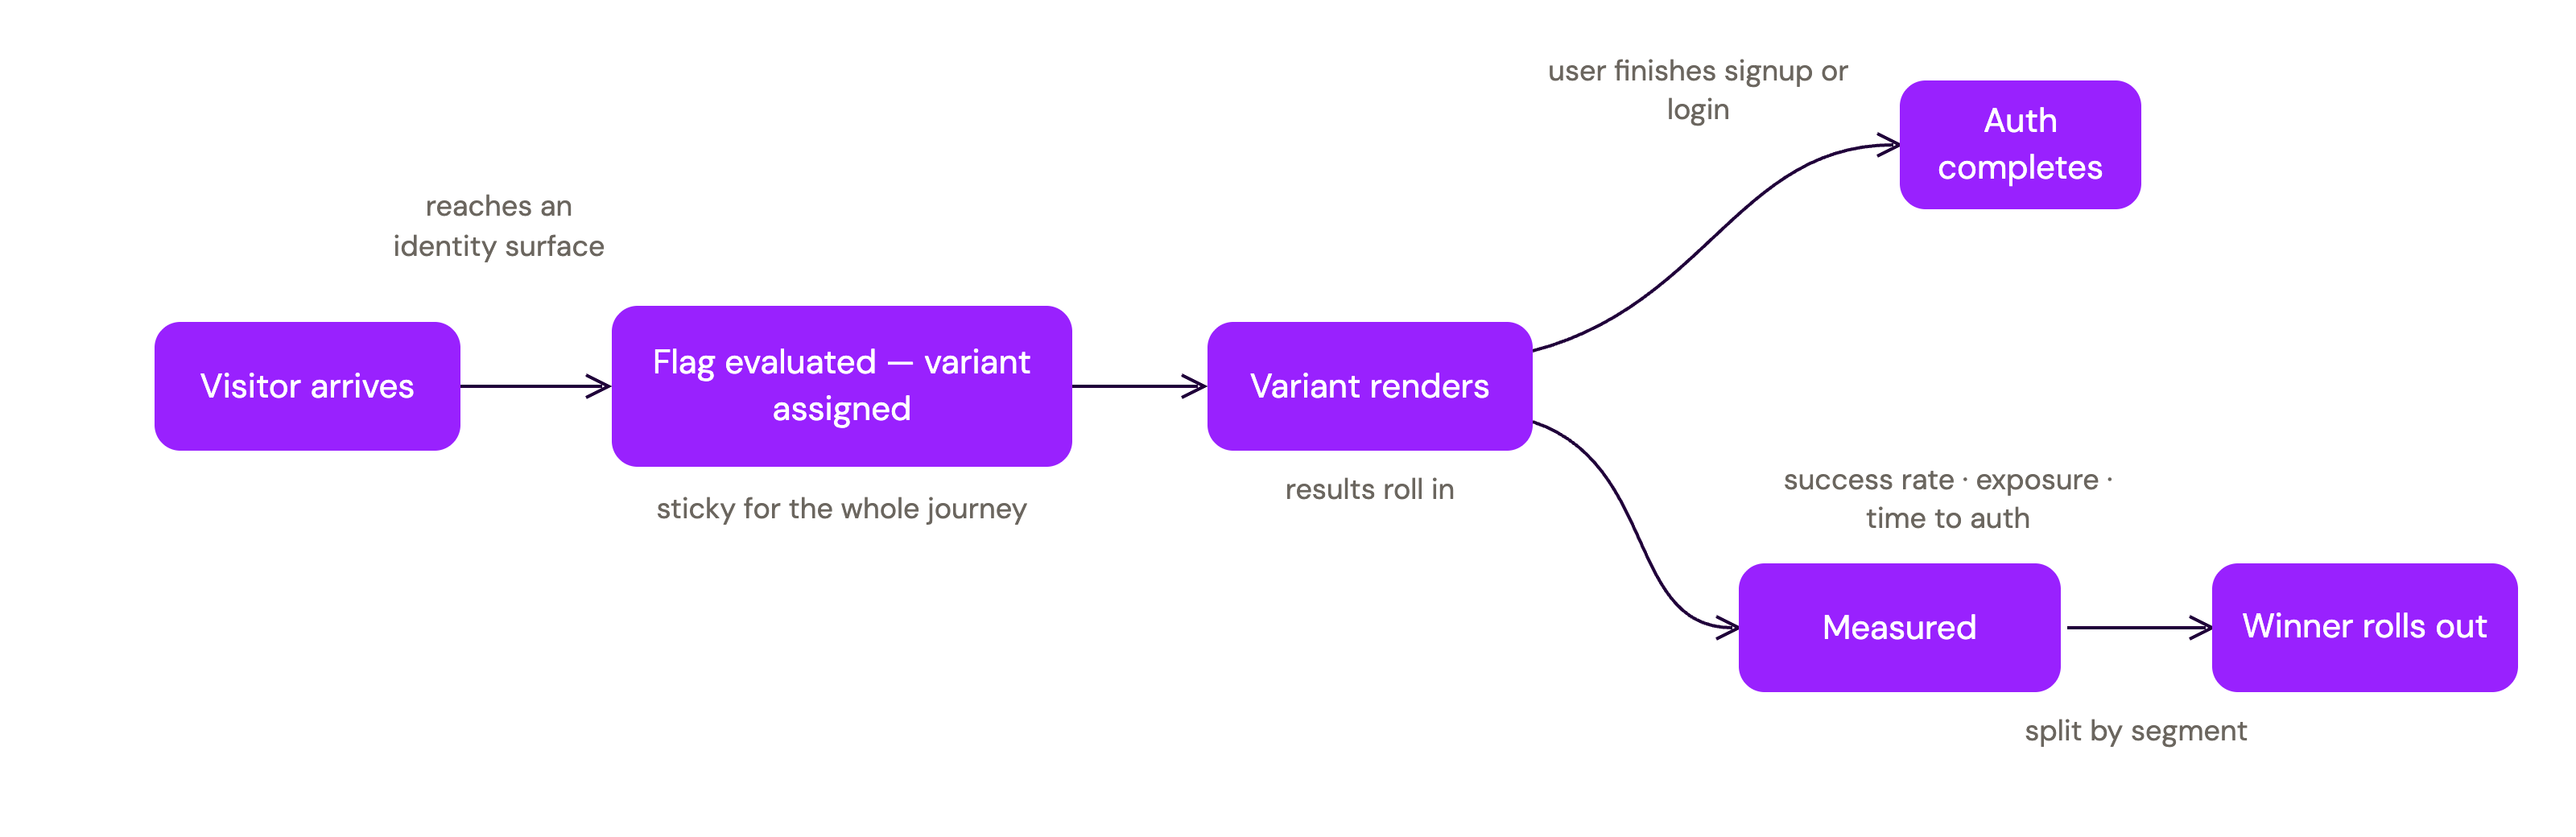
Adds Anonymous Sessions to maintain session context for visitors before they sign up or log in.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Identity Conversion Suite is now in Early Access (2026-10-26) · Oct 2026
· source
· release history
-
Both Anonymous Sessions and Experiment Center are available in Early Access to Auth0 Enterprise plan customers.
 announced · Sep 2026
· source
· release history
- Adds Anonymous Sessions: issues OAuth 2.0-compliant access tokens to unauthenticated guest users, enabling guest checkout, cart tracking, pre-login personalization, and secure API access without authentication — with seamless transfer of anonymous metadata into the authenticated profile on sign-up or login. announced · Sep 2026 · source · release history
-
Passes the anonymous session token to the Auth0
/authorizeendpoint on sign-up or login, making all prior anonymous activity available inside Actions for custom handling.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Sep 2026 · source · release history -
Anonymous sessions can be linked to authenticated users through pre-registration and post-login actions, preserving cross-device activity on the authenticated profile.
changelog · Jul 2026
· source
· release history
-
New Anonymous Sessions (beta, paid plans): create and manage stateless sessions for unauthenticated users via a new
POST /anonymous/tokenendpoint supporting guest checkout, cart persistence, and pre-login personalization. changelog · Jul 2026 · source · release history
docs
- The Auth0 Identity Conversion Suite bundles two Auth0 features that solve complementary problems: Anonymous Sessions : Track and manage users from their first pre-authentication interaction and carry that activity to their authenticated profile when they sign up or log in. docs update · Sep 2026 · source
example
-
Trigger an anonymous session and obtain an OAuth 2.0 access token for a guest user before they authenticate, so cart and wishlist metadata is tracked from first interaction.
Pass referral IDs, shopping cart IDs, or wishlist URLs to Auth0 at the start of the guest session.announced · Sep 2026 · source -
Enable anonymous sessions for your tenant and a specific application so guest activity is tracked before login.
In the Auth0 Dashboard, go to Settings > (Tenant Settings) and enable Anonymous Sessions length configuration, then navigate to Applications > <your app> > Settings and enable Anonymous Sessions for…changelog · Jul 2026 · source -
Enable anonymous sessions for a specific application and API, and set session length, via the Auth0 dashboard.
In the Auth0 dashboard, go to Applications > <your application> and enable Anonymous Sessions. Then go to APIs > <your API> and enable Anonymous Sessions.Anonymous sessions are now in beta! (2026-07-20) · Jul 2026 · source
Cross App Access (XAA) shipped Passes authorization across domains so AI agents and enterprise apps can securely access MCP servers and APIs without per-user consent prompts, with centralised IT governance over cross-application data-sharing connections.
release 12 total
-
Auth0 now supports acting as a requesting application in Cross-App Access flows (Early Access), built on Auth0 Token Vault using the ID-JAG (Identity Assertion Authorization Grant) protocol, allowing apps to fetch third-party API tokens for enterprise users without requiring manual Connect your account steps;…
changelog · Sep 2026
· source
· release history
- Adds a new Dashboard toggle to enable Cross-App Access Requesting App on enterprise connections. changelog · Sep 2026 · source · release history
-
Adds self-service configuration of the Cross App Access (XAA) Resource Application role for a connection via the My Organization API and Embeddable UI Components.
My Organization API and Embeddable UI Components - XAA and third-party app access configuration in Early Acces (2026-09-03) · Sep 2026
· source
· release history
- Enables XAA configuration with a domain-verification guardrail: the connection's identity provider must use a domain verified for the associated Organization, scoping cross-app authorization to providers the customer controls. My Organization API and Embeddable UI Components - XAA and third-party app access configuration in Early Acces (2026-09-03) · Sep 2026 · source · release history
- New Dashboard toggle on enterprise connections enables the Cross-App Access Requesting App flow, letting apps silently fetch third-party API tokens for authenticated users without requiring per-integration Connect your account clicks. Cross-App Access Requesting App now in Early Access (2026-08-31) · Aug 2026 · source · release history
- Adds support for acting as a requesting application in Cross-App Access flows using the ID-JAG protocol Cross-App Access Requesting App now in Early Access (2026-08-31) · Aug 2026 · source · release history
docs
- September 3, 2026 Version 202636 We're excited to announce that self-service configuration of Third-Party Application Access and Cross App Access (XAA) is now available through the My Organization API and Embeddable UI Components, in Open Early Access. changelog · Sep 2026 · source
- Third-party application access settings for Organizations and their connections Cross App Access (XAA) Resource Application settings for connections third_party_client_access Object. Controls which values Organization Admins can set for third-party application access on this Organization via the My Organization API. docs update · Sep 2026 · source
example
-
Enable Cross-App Access Requesting App on an enterprise OIDC connection so your app can fetch third-party API tokens for org users without a manual consent step.
In the Auth0 Dashboard, go to Authentication > Enterprise Connections, select your OIDC or Okta Workforce connection, and toggle 'Cross-App Access Requesting App' to enabled.changelog · Sep 2026 · source -
Enable the requesting app capability on an enterprise connection via the Dashboard UI.
In the Auth0 Dashboard, navigate to your Enterprise Connection settings and enable the 'Cross-App Access Requesting App' toggle.Cross-App Access Requesting App now in Early Access (2026-08-31) · Aug 2026 · source
Database Connection Password Policy shipped Provides granular password composition controls for database connections — minimum length (defaulting to 15 for new connections), required character types, sequential/repeated character blocking, and profile-data rejection — with a unified `password_options` API that rejects mixed legacy and new fields.
release 15 total
-
New database connections created from July 2026 onward default to Flexible Password Policy with a minimum password length of 15, no required character types, and no legacy fields — applies whether the connection is created via Dashboard, Management API, Deploy CLI, Terraform, or an Auth0 SDK.
changelog · Aug 2026
· source
· release history
- New database connections created from July 2026 default to Flexible Password Policy (minimum length 15, no required character types) rather than legacy password policy defaults. changelog · Aug 2026 · source · release history
-
PATCH /api/v2/connections/{id}returns400 invalid_bodyif the request body includes bothpassword_optionsand legacy password fields (passwordPolicy,password_complexity_options,password_history,password_no_personal_info,password_dictionary). changelog · Aug 2026 · source · release history -
Adds
options.password_optionsobject to database connections, replacing legacy fields (passwordPolicy,password_complexity_options,password_history,password_no_personal_info,password_dictionary) with granular controls for composition, history, dictionary (10,000- or 100,000-word lists plus custom… changelog · Aug 2026 · source · release history -
New database connections created without an explicit password configuration now default to
options.password_optionswith a minimum password length of 15 (up from legacy defaults) — pipelines that create connections and expect legacy defaults will receive the new NIST-aligned defaults instead. Flexible Password Policy is now generally available (2026-08-13) · Aug 2026 · source · release history -
Adds profile-data blocking in
options.password_optionsto reject passwords containing values from user profile fields, with a configurable field list. Flexible Password Policy is now generally available (2026-08-13) · Aug 2026 · source · release history
docs
- August 13, 2026 Flexible Password Policy is now generally available The Flexible Password Policy for database connections is now generally available. changelog · Aug 2026 · source
B2B Organization Member Management shipped Provides APIs and embeddable UI components to list members, send bulk invitations with role assignments, and manage member roles and access levels within an organization.
Also counts toward: Role-based access control, REST API
release 13 total
-
Adds permission-aware UI components that show or hide actions based on the authenticated user's effective permissions surfaced from the ID token, with no additional API call required.
changelog · Sep 2026
· source
· release history
-
Adds the My Organization API and Embeddable UI Components for B2B member management, supporting member invitations (bulk up to 10 per request), role assignment, and a four-tier access level model (
none,readonly,limited,full). changelog · Sep 2026 · source · release history -
Adds api.user.setUserId() method callable inside a
pre-user-registrationAction to assign a customuser_id— UUIDs, domain-specific IDs, or legacy-compatible IDs — to new database-connection users at signup, replacing the automaticauth0|<id>format.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Custom User ID Assignment with Actions — Early Access (2026-09-17) · Sep 2026
· source
· release history
- Adds member listing and retrieval through the My Organization API with field projection and checkpoint-based pagination for large organizations. My Organization API and Embeddable UI Components - Member Management in Early Access! (2026-09-17) · Sep 2026 · source · release history
- Emits tenant log events for all member, invitation, and role operations for full B2B observability of administrative activity. My Organization API and Embeddable UI Components - Member Management in Early Access! (2026-09-17) · Sep 2026 · source · release history
- Adds Member Invitations capability allowing administrators to invite new members by email with pre-assigned roles and identity provider routing in bulk (up to 10 per atomic request). My Organization API and Embeddable UI Components - Member Management in Early Access! (2026-09-17) · Sep 2026 · source · release history
example
-
Activate the My Organization API to enable self-service B2B member management for organization administrators.
In the Auth0 Dashboard, go to Applications > APIs, locate the My Organization API, and activate it for your tenant.changelog · Sep 2026 · source
Auth0 CLI Agent Mode shipped Runs the Auth0 CLI in a mode designed for unattended AI-agent use, providing structured JSON output, no interactive prompts, and a reliable exit code on every failure.
Also counts toward: Command-line interface, JSON data export
release 7 total
-
Adds
--agent-modeflag (orAUTH0_AGENT_MODE=trueenv var) for structured JSON output, prompt-free operation, guaranteed non-zero exit on failure, and stable errorcode/reasonfields (auto-detected for recognized agent clients);auth0 commands --flat(with optional--detailed) for full CLI discovery in a…
changelog · Oct 2026
· source
· release history
-
Adds
auth0 commands --flatsubcommand for full CLI discovery in one call; append--detailedfor complete invocation shapes.
Agent Mode for the Auth0 CLI (2026-10-21) · Oct 2026
· source
· release history
-
Adds
--dataflag to send an entire payload as one JSON object, validated locally before it reaches the API. Agent Mode for the Auth0 CLI (2026-10-21) · Oct 2026 · source · release history -
Structured errors now carry a stable
code, a finerreason, and field-level detail on validation errors instead of a free-text sentence. Agent Mode for the Auth0 CLI (2026-10-21) · Oct 2026 · source · release history -
Adds
--agent-modeflag (orAUTH0_AGENT_MODE=trueenv var) to enable structured JSON output, disable prompts and color, and guarantee non-zero exit codes on failure — auto-detected for recognized agent clients.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Agent Mode for the Auth0 CLI (2026-10-21) · Oct 2026 · source · release history -
Adds
--schemaflag to print the exact payload a command expects, sourced live from the OpenAPI spec. Agent Mode for the Auth0 CLI (2026-10-21) · Oct 2026 · source · release history
docs
- Auth0 CLI The Auth0 CLI’s Agent Mode makes it predictable for an AI agent to drive unattended directly from your terminal. Agent Mode has structured JSON output, no interactive prompts, and a reliable exit code on every failure. docs update · Oct 2026 · source
example
-
Discover every available CLI command and its full invocation shape in one call, useful for feeding an agent its action space.
auth0 commands --flat --detailedAgent Mode for the Auth0 CLI (2026-10-21) · Oct 2026 · source -
Run the CLI in a keychain-free CI environment using only environment variables — no disk writes, no interactive prompts.
export AUTH0_CLI_AUTH_MODE=env export AUTH0_DOMAIN=<your-auth0-domain> export AUTH0_API_TOKEN=<management-api-token> auth0 apps list --agent-mode --json-compactannounced · Oct 2026 · source -
Let an agent discover the full CLI surface and create a resource safely in a single session, without guessing field names.
auth0 apps create --schema auth0 apps create --agent-mode --data '{"name":"billing-app","app_type":"spa"}'announced · Oct 2026 · source -
Filter a log list by query parameters without memorising per-command flags — useful for agents building dynamic queries.
auth0 logs list --agent-mode --query '{"per_page":5}'announced · Oct 2026 · source
Organizations Search and Filtering shipped Provides advanced filtering of the Organizations list by Name, Display Name, ID, Metadata key-value pairs, third-party client access policy, and app entitlement status, with up to 5 simultaneous AND/OR filters and filter state persisted in a shareable URL.
release 7 total
-
Organizations Search now supports advanced filtering on Name, Display Name, ID, Metadata (custom key-value pairs), third-party client access policy (allow or block), and app entitlement status.
changelog · Aug 2026
· source
· release history
- Up to 5 organization filters can be combined simultaneously using AND/OR logic, with filter state persisted in the URL for sharing or bookmarking. changelog · Aug 2026 · source · release history
-
Adds Display name,
ID, Metadata, Third-party client access, and App entitlement active filter options to the Organizations Search bar in the Auth0 Dashboard Organizations Search Expands with Advanced Filtering (2026-08-04) · Aug 2026 · source · release history - Adds filtering by Name, Display name, ID, Metadata (custom key-value pairs), Third-party client access (allow or block), and App entitlement active status in the Organizations Search interface. Organizations Search Expands with Advanced Filtering (2026-08-04) · Aug 2026 · source · release history
- Filter pills persist in the URL, enabling shareable and bookmarkable filtered Organization views. Organizations Search Expands with Advanced Filtering (2026-08-04) · Aug 2026 · source · release history
- Supports combining up to 5 filters simultaneously with AND/OR logic. Organizations Search Expands with Advanced Filtering (2026-08-04) · Aug 2026 · source · release history
example
-
Filter your tenant's Organizations list to find orgs with a specific metadata tag and third-party client access blocked, then share the view via URL.
Navigate to Auth0 Dashboard > Organizations, open the search bar, add a Metadata filter (e.g.changelog · Aug 2026 · source -
Find all organizations where a specific metadata key is set and third-party client access is blocked — useful for auditing tenant isolation policies.
In the Auth0 Dashboard, go to Organizations > search bar, add a Metadata filter (e.g.Organizations Search Expands with Advanced Filtering (2026-08-04) · Aug 2026 · source -
Quickly find all active organizations with specific third-party access policies via the dashboard UI.
In the Auth0 Dashboard, go to Organizations and type filters: `Display name` contains 'Acme', `App entitlement active` equals true, then save the view.Organizations Search Expands with Advanced Filtering (2026-08-04) · Aug 2026 · source
API search in Dashboard shipped Real-time search for APIs by ID, identifier, or name in the Auth0 Dashboard, replacing paginated list scrolling.
Also counts toward: Web management console
release
-
Adds Global Search (Beta) to the Command Palette (Cmd+K), enabling real-time tenant-wide search across Applications, APIs, Organizations, and Users by name, ID, email, or identifier with one-click ID copying.
changelog · Aug 2026
· source
· release history
- View more links from search results navigate directly to filtered entity lists for deeper exploration. Global Search in Cmd+K is now in Beta (2026-07-31) · Jul 2026 · source · release history
- Adds Global Search via the Command Palette (Cmd+K) to search Applications, APIs, Organizations, and Users by name, ID, email, or identifier Global Search in Cmd+K is now in Beta (2026-07-31) · Jul 2026 · source · release history
- New Global Search in Command Palette (Cmd+K) lets you search Applications, APIs, Organizations, and Users by name, ID, email, or identifier in real time. Global Search in Cmd+K is now in Beta (2026-07-31) · Jul 2026 · source · release history
- One-click identifier copying from search results lets you instantly grab entity IDs without navigating to detail pages. Global Search in Cmd+K is now in Beta (2026-07-31) · Jul 2026 · source · release history
- Adds real-time search for APIs in the Auth0 Dashboard, allowing lookup by API ID, identifier, or name (Public Beta, rolling out to Public Cloud tenants). Dashboard Search for APIs Now in Beta (2026-06-15) · Jun 2026 · source · release history
docs
- July 31, 2026 Global Search in Cmd+K is now in Beta We're excited to announce that Global Search is now in Beta, bringing entity search directly to the Command Palette (Cmd+K). changelog · Aug 2026 · source
example
-
Find a specific user or application across your tenant instantly without navigating menus.
In the Auth0 Dashboard, press Cmd+K (or Ctrl+K), then type the user's email address or application name to search across Applications, APIs, Organizations, and Users in real time.changelog · Aug 2026 · source -
Quickly locate a user by email or ID during an incident without leaving your current page.
Press Cmd+K, type the user's email or client ID, and select the matching result to navigate directly to that entity or copy its identifier.Global Search in Cmd+K is now in Beta (2026-07-31) · Jul 2026 · source -
Quickly locate a specific API in large tenants without paging through lists.
In the Auth0 Dashboard, go to Applications > APIs and type the API name, identifier, or ID into the search bar to filter results in real time.Dashboard Search for APIs Now in Beta (2026-06-15) · Jun 2026 · source
Auth0 Portals shipped Hosts pre-built consumer and business portals on your domain where end users can update profiles, enroll MFA factors and passkeys, and review security settings, and where organization administrators can edit organization details and verify domains — with visual page building via Universal Components and Auth0 Forms, tenant or organization branding, MFA step-up handling, and server-side token storage so browsers receive only a session cookie.
Also counts toward: Multi-factor authentication
release 7 total
-
Portals automatically trigger an MFA step-up challenge when Auth0 requires MFA for an operation, then retry the operation once the user completes it.
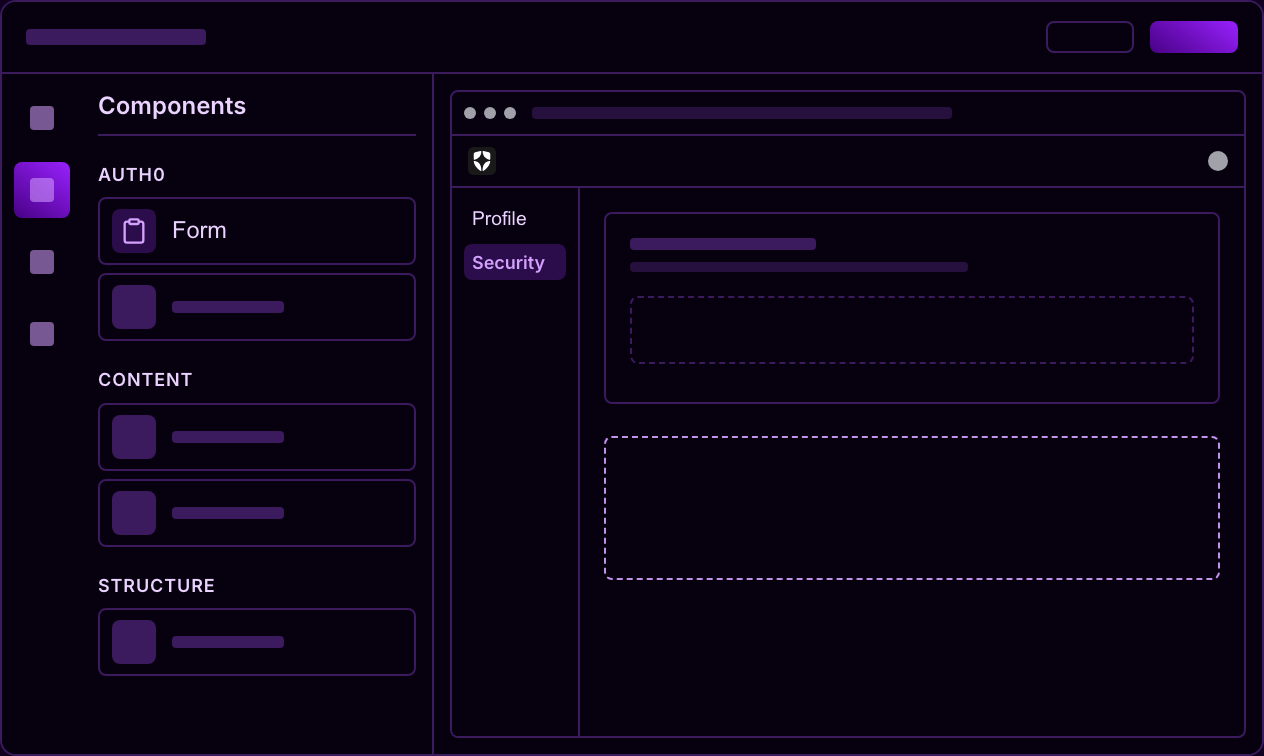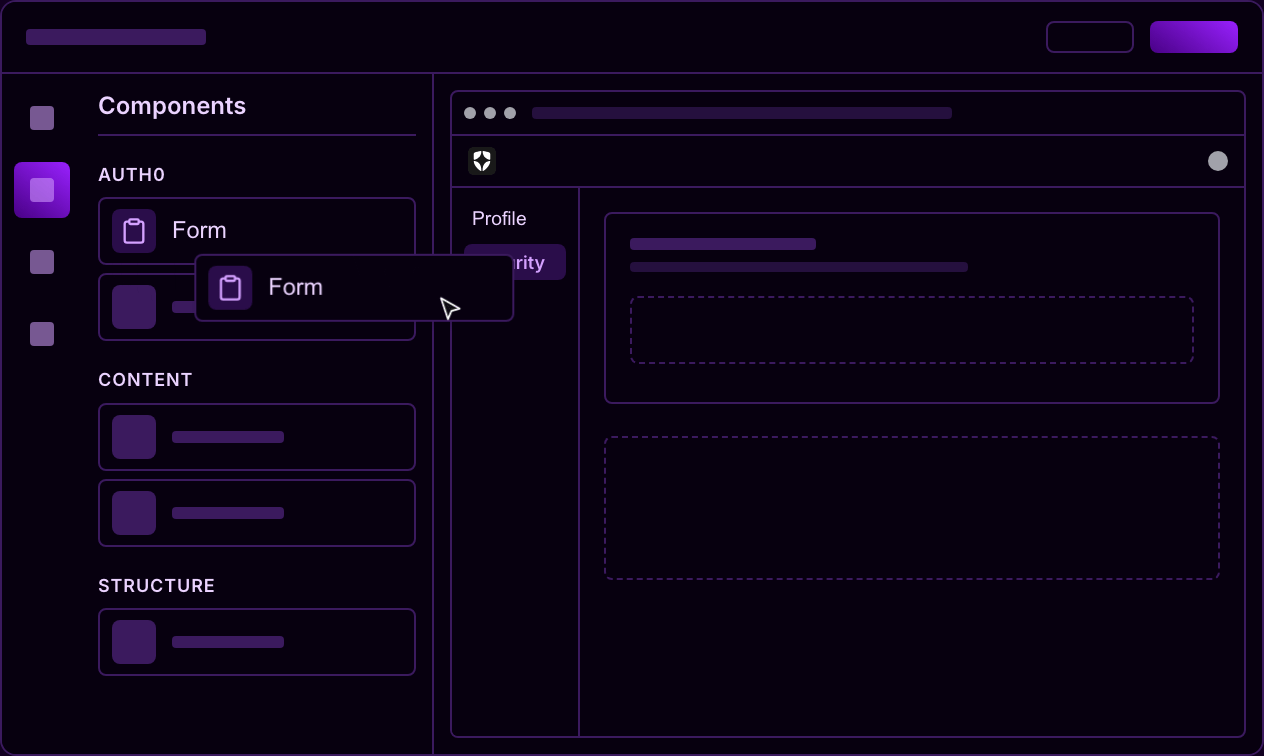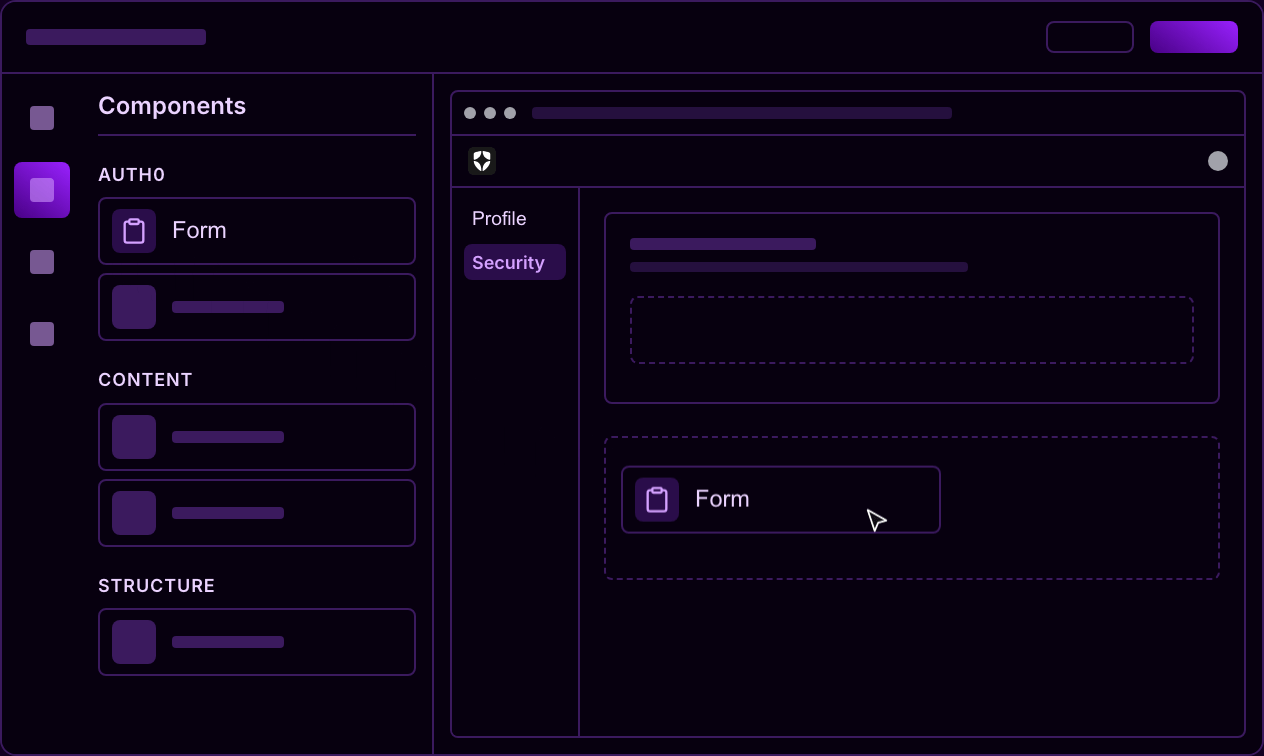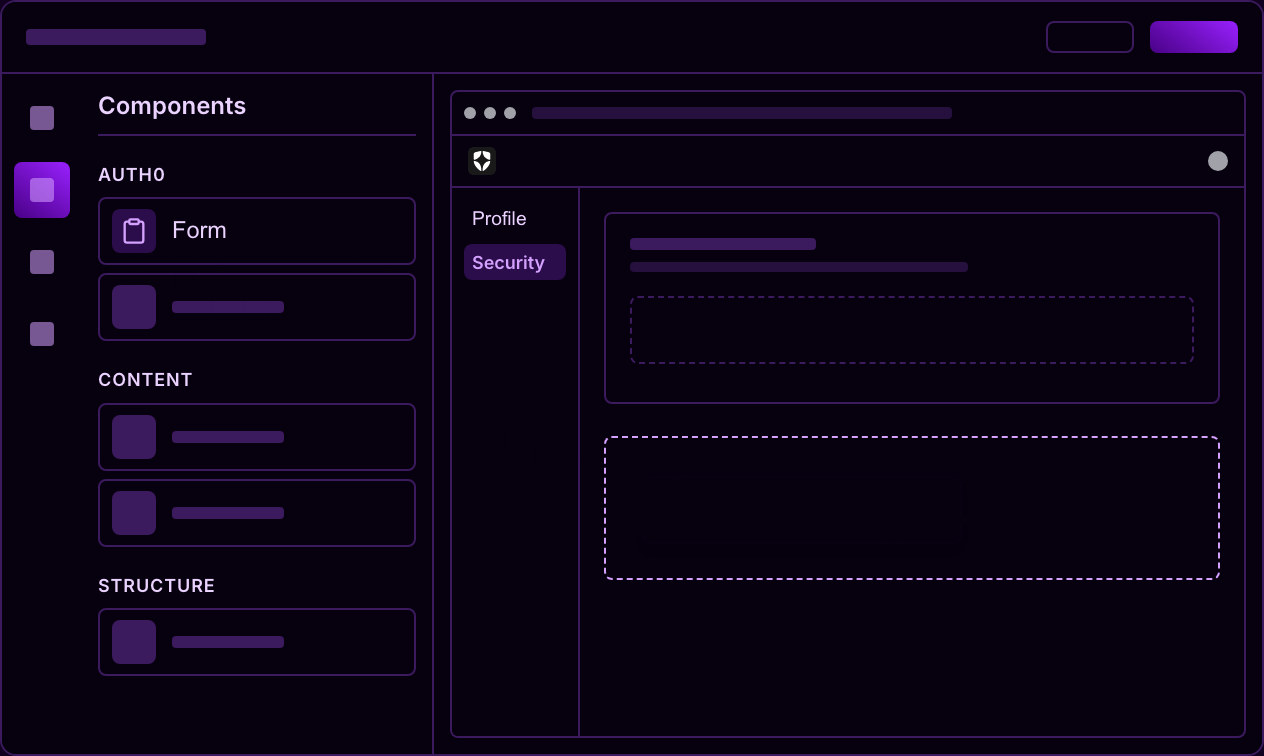 Introducing Universal Portals - Developer Preview (2026-10-27) · Oct 2026
· source
· release history
- Add an Auth0 Form to any portal page to collect or update information, including profile updates, policy acceptance, and communication preferences. Introducing Universal Portals - Developer Preview (2026-10-27) · Oct 2026 · source · release history
- Auth0 now offers consumer portals where end users can update their profile, enroll MFA factors and passkeys, and review security settings — hosted by Auth0 on your domain with no interface to build or maintain.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Introducing Universal Portals - Developer Preview (2026-10-27) · Oct 2026 · source · release history
- Build portal pages visually using Universal Components, Auth0 Forms, and layout components such as headings, rich text, sections, separators, and images. Introducing Universal Portals - Developer Preview (2026-10-27) · Oct 2026 · source · release history
- Portals inherit your tenant's logo, colors, and fonts — or switch to an organization's branding when opened in an organization context. Introducing Universal Portals - Developer Preview (2026-10-27) · Oct 2026 · source · release history
- Auth0 now offers business portals where organization administrators can edit organization details and verify domains, without custom development. Introducing Universal Portals - Developer Preview (2026-10-27) · Oct 2026 · source · release history
example
-
Set up a consumer portal so end users can self-serve MFA enrollment and profile updates without you building any UI.
In the Auth0 dashboard, go to Customize > Portals, create a new portal of type 'Consumer', add a Universal Component for MFA enrollment, and publish it to your tenant domain.Introducing Universal Portals - Developer Preview (2026-10-27) · Oct 2026 · source -
Embed an Auth0 Form on a portal page to collect policy acceptance from users on login.
In the Auth0 dashboard, go to Customize > Portals, open a portal page in the visual builder, select 'Add Component > Auth0 Form', choose your policy-acceptance Form, and save.Introducing Universal Portals - Developer Preview (2026-10-27) · Oct 2026 · source
Terraform B2B SaaS Starter Module shipped A Terraform module available on the Terraform Registry that provisions a complete B2B SaaS identity foundation — app client, API, RBAC, MFA, attack protection, and branding — from a single module block, with opinionated security defaults, role and permission declarations with pre-apply validation, multi-instance tenant-ownership controls, custom domain verification support, and 12 ready-to-run example configurations.
Also counts toward: Multi-factor authentication, Multi-tenant management, Role-based access control
release
-
Adds
custom_domainandenable_custom_domain_verificationinputs withdns_verification_record,dns_verification_command, andcustom_domain_next_stepoutputs to guide multi-step custom-domain verification. announced · Oct 2026 · source · release history - Ships 12 ready-to-run example configurations in the GitHub repository covering minimal SPA, APIs and RBAC, SAML/OIDC enterprise SSO, multi-application tenants, and a full-featured setup. announced · Oct 2026 · source · release history
-
Applies security defaults automatically on first apply: RBAC enforcement (
enforce_policies = true,token_dialect = "access_token_authz"), PKCE with rotating refresh tokens and a three-second grace period, brute-force protection, suspicious IP throttling, breached password detection, and TOTP-based MFA with email… announced · Oct 2026 · source · release history -
Adds
manage_tenant,manage_attack_protection, andmanage_mfaboolean inputs so multiple module instances on the same tenant can each opt out of owning tenant-wide settings. announced · Oct 2026 · source · release history -
Adds
rolesandpermissionsmap inputs to the module so role and permission definitions can be declared as plain data, with pre-apply validation that catches references to undeclared roles before any Auth0 resources change. announced · Oct 2026 · source · release history -
Adds the
b2b-saas-starterTerraform module (auth0/modules/auth0//modules/b2b-saas-starter), available on the Terraform Registry, that provisions a complete B2B SaaS identity foundation — app client, API, RBAC, MFA, attack protection, and branding — from a singlemoduleblock.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Oct 2026 · source · release history
example
-
Add a second application (e.g. an admin portal) to the same tenant without conflicting over tenant-wide MFA and attack-protection settings.
module "admin_portal" { source = "auth0/modules/auth0//modules/b2b-saas-starter" version = "~> 1.0" app_name = "Acme Admin" app_callbacks = ["https://admin.acme.com/callback"] app_logout_urls =…announced · Oct 2026 · source -
Bootstrap a full B2B SaaS identity stack — app, API, RBAC, MFA, and attack protection — in one apply.
module "b2b_saas" { source = "auth0/modules/auth0//modules/b2b-saas-starter" version = "~> 1.0" app_name = "Acme" app_callbacks = ["https://app.acme.com/callback"] app_logout_urls =…announced · Oct 2026 · source -
Onboard a new enterprise customer with SAML SSO without touching any other tenant settings.
module "b2b_saas" { source = "auth0/modules/auth0//modules/b2b-saas-starter" version = "~> 1.0" app_name = "Acme" app_callbacks = ["https://app.acme.com/callback"] app_logout_urls =…announced · Oct 2026 · source
Auth0 plugin for ChatGPT shipped A ChatGPT plugin that connects to a real Auth0 tenant so users can create applications, configure connections, adjust settings, query tenant state, generate tenant-matched SDK integration code, and get documentation answers — all via plain-language prompts inside a ChatGPT session.
Also counts toward: Natural-language query
release 7 total
- Enables querying and managing tenant state — applications, users, and connections — from within a ChatGPT session without opening the Auth0 dashboard. announced · Sep 2026 · source · release history
- New Auth0 plugin for ChatGPT (findable via the ChatGPT plugins directory) connects to a real Auth0 tenant to create applications, configure connections, and adjust settings by plain-language prompt.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Sep 2026 · source · release history
- Generates tenant-matched SDK integration code instead of generic boilerplate, so the output compiles against the caller's actual Auth0 configuration. announced · Sep 2026 · source · release history
- Surfaces Auth0 documentation answers directly inside the ChatGPT conversation. announced · Sep 2026 · source · release history
-
Adds Dashboard support to create and manage Custom Token Exchange Profiles and their associated Actions directly from the Auth0 Dashboard.
Custom Token Exchange is now Generally Available (2026-08-28) · Aug 2026
· source
· release history
- Adds shared transaction context: set transaction metadata in a Custom Token Exchange Action and read it from a Post-Login Action to customize resulting tokens based on subject or actor token information. Custom Token Exchange is now Generally Available (2026-08-28) · Aug 2026 · source · release history
example
-
Bootstrap auth for a new web app without leaving ChatGPT — the plugin creates the Auth0 application in your real tenant and returns working SDK setup code.
Set up a new @Auth0 application for my web app and add login.announced · Sep 2026 · source -
Create and configure a Custom Token Exchange Profile and its Action directly from the Dashboard to support AI-agent delegated authorization.
1. In the Auth0 Dashboard, go to Actions > Custom Token Exchange Profiles. 2. Click 'Create Profile' and specify the subject token type (Auth0 or external IdP). 3.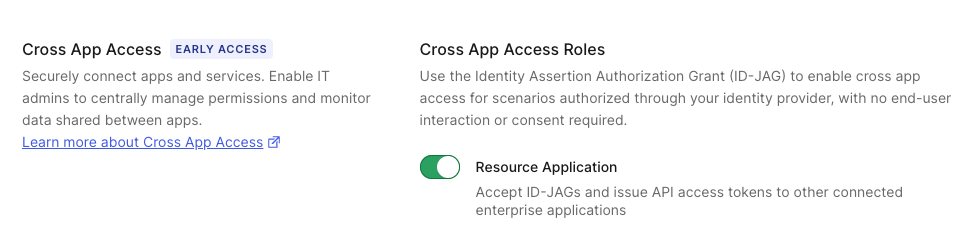 changelog · Aug 2026
· source
Action Modules shipped Enables the creation and reuse of custom code modules across multiple Actions and Triggers with independent secrets, dependencies, and IntelliSense support.
release 9 total
-
Adds Action Modules, enabling reuse of custom functions across multiple Actions and Triggers, with independent secrets and dependencies per module.
changelog · Sep 2026
· source
· release history
-
Adds unit testing support for Action Modules via helpers in the
@auth0/actionspackage. changelog · Sep 2026 · source · release history -
Action Modules support cross-trigger access to reuse custom functions across multiple Actions and Triggers.
Actions - Modules - GA (2026-09-18) · Sep 2026
· source
· release history
- Each Action Module can define independent secrets and dependencies, allowing isolated configuration per module. Actions - Modules - GA (2026-09-18) · Sep 2026 · source · release history
- Introduces Actions Modules — create, manage, and share reusable code across multiple Actions and Triggers within an Auth0 Tenant. Actions - Modules - GA (2026-09-18) · Sep 2026 · source · release history
- Enables cross-trigger reuse of custom functions by importing a single Module into any Action regardless of which Trigger it is bound to. Actions - Modules - GA (2026-09-18) · Sep 2026 · source · release history
Third-party application access for Organizations shipped Controls whether third-party apps can authenticate users within an Auth0 Organization, scoping consent per organization with opt-in enablement and domain-level connection requirements.
release 7 total
-
Adds self-service configuration of Third-Party Application Access and Cross App Access (XAA) through the My Organization API and Embeddable UI Components (Open Early Access), letting Organization Admins configure third-party app access, connection-level third-party access, and XAA Resource Application roles without…
changelog · Sep 2026
· source
· release history
-
Adds self-service configuration of third-party application access for an Organization via the My Organization API and Embeddable UI Components, so Organization Admins can manage access without routing changes through the Auth0 Dashboard.
My Organization API and Embeddable UI Components - XAA and third-party app access configuration in Early Acces (2026-09-03) · Sep 2026
· source
· release history
- Adds self-service configuration of third-party application access for a specific connection of an Organization through the My Organization API and Embeddable UI Components. My Organization API and Embeddable UI Components - XAA and third-party app access configuration in Early Acces (2026-09-03) · Sep 2026 · source · release history
- Enables third-party application access for Auth0 Organizations, configurable on a per-organization basis by tenant admins. Third-Party Apps for Organizations is now Generally Available (2026-07-10) · Jul 2026 · source · release history
- Blocks third-party app access by default for all existing organizations — admins must explicitly opt in, preserving backward compatibility. Third-Party Apps for Organizations is now Generally Available (2026-07-10) · Jul 2026 · source · release history
- Scopes user consent per organization — consent granted in one organization does not propagate to others. Third-Party Apps for Organizations is now Generally Available (2026-07-10) · Jul 2026 · source · release history
example
-
Enable third-party app access for a specific organization after opting in (access is blocked by default).
In the Auth0 Dashboard, go to Organizations > <your-org> > Settings and enable third-party application access for that organization.Third-Party Apps for Organizations is now Generally Available (2026-07-10) · Jul 2026 · source -
Promote a connection to domain level so a third-party app can authenticate users within a specific organization.
curl --request PATCH \ --url 'https://<tenant>.auth0.com/api/v2/connections/<connection_id>' \ --header 'Authorization: Bearer <mgmt_api_token>' \ --header 'Content-Type: application/json' \ --data…Third-Party Apps for Organizations is now Generally Available (2026-07-10) · Jul 2026 · source
DPoP Sender-Constrained Token Binding shipped Allows enforcement of DPoP to bind access tokens to the requesting client, preventing replay attacks from stolen tokens.
release
-
Introduces Application Profiles in Early Access, enabling centralized governance of security settings (refresh token lifetimes, leeway, DPoP, B2B login behavior) across all CIMD-registered applications from a single configuration point in the Auth0 Dashboard under the Applications section.
changelog · Oct 2026
· source
· release history
-
Adds Application Profiles (Early Access) to govern security settings — refresh token lifetimes, leeway, and DPoP — across all DCIMD applications from a single configuration point.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Application Profiles are available in Early Access (2026-10-22) · Oct 2026
· source
· release history
- Introduces Application Profiles (Early Access) to centrally manage refresh token policies, DPoP, and Organizations for dynamically registered CIMD clients. CIMD with Dynamic Registration in Early Access (2026-10-22) · Oct 2026 · source · release history
- Adds Application Profiles (Early Access) for centrally managing security and authorization settings — including refresh token policies, Demonstrating Proof of Possession (DPoP), and Organizations — across dynamically registered CIMD clients. announced · Oct 2026 · source · release history
-
Adds DPoP (RFC 9449) sender-constrained token binding by setting
useDPoP = trueon Auth0Account. announced · Oct 2026 · source · release history
example
-
Configure Application Profiles for DCIMD apps via the Auth0 dashboard to enforce uniform refresh token and DPoP settings across all AI agent-managed applications.
1. In the Auth0 dashboard, navigate to Applications section. 2. Open 'Application Profiles'. 3. Set default values for refresh token lifetimes, leeway, and DPoP. 4.Application Profiles are available in Early Access (2026-10-22) · Oct 2026 · source -
Enable DPoP sender-constrained tokens so a stolen access token cannot be replayed from another app or device.
import com.auth0.kmp.Auth0 import com.auth0.kmp.core.Auth0Account val account = Auth0Account( clientId = "<YOUR_CLIENT_ID>", domain = "<YOUR_DOMAIN>", useDPoP = true ) val auth0 = Auth0(account)announced · Oct 2026 · source
Connection Event Subscriptions shipped Enables subscription to creation, update, and deletion events for enterprise connections to eliminate the need for API polling.
Also counts toward: Outbound webhooks (the product notifies you)
release 7 total
-
Adds
connection.created,connection.updated, andconnection.deletedevents for enterprise connections (Azure AD, ADFS, Google Workspace, Active Directory, LDAP, Ping), deliverable to a webhook or Amazon EventBridge as CloudEvents-formatted JSON.
changelog · Sep 2026
· source
· release history
-
Adds
connection.created,connection.updated, andconnection.deletedevent subscriptions for enterprise connections (Azure AD, ADFS, Google Workspace, Active Directory, LDAP, and Ping), eliminating the need to poll the Management API for connection changes.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Enterprise Connection Events — Early Access (2026-09-16) · Sep 2026
· source
· release history
- Enables delivery of these events to a webhook or Amazon EventBridge via CloudEvents-formatted JSON Enterprise Connection Events — Early Access (2026-09-16) · Sep 2026 · source · release history
- Streams enterprise connection events (created, updated, deleted) to a webhook, Amazon EventBridge, or a custom event pipeline.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ B2B Connect - Enterprise in Early Access! (2026-09-16) · Sep 2026 · source · release history
-
Adds
stream_connection_eventscapability to push created/updated/deleted enterprise connection events to a webhook endpoint or Amazon EventBridge pipeline for real-time visibility. B2B Connect - Enterprise in Early Access! (2026-09-16) · Sep 2026 · source · release history -
Adds subscription to
connection.created,connection.updated, andconnection.deletedevents for enterprise connections Enterprise Connection Events — Early Access (2026-09-16) · Sep 2026 · source · release history
Outbound SCIM provisioning via Event Streams shipped Pushes Auth0 user lifecycle events to any SCIM 2.0-compliant downstream application using a built-in Action template, with attribute mapping, opt-in UPSERT behavior, and native fault tolerance — no custom webhook infrastructure required.
Also counts toward: SCIM provisioning API
release
-
Adds
connection.created,connection.updated, andconnection.deletedevent subscriptions for enterprise connections (Azure AD, ADFS, Google Workspace, Active Directory, LDAP, and Ping), eliminating the need to poll the Management API for connection changes.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Enterprise Connection Events — Early Access (2026-09-16) · Sep 2026
· source
· release history
- Provision users outbound via SCIM wired to federated connections. Enterprise Connect - Beta (2026-07-30) · Jul 2026 · source · release history
- Built-in fault tolerance handles API timeouts and retries for transient failures natively within the Action script. Automate Downstream Provisioning with Outbound SCIM for Users via Event Streams (2026-07-01) · Jul 2026 · source · release history
-
Supports SCIM 2.0 REST operations (
POST,PUT,DELETE) translated directly from Auth0 user lifecycle events. Automate Downstream Provisioning with Outbound SCIM for Users via Event Streams (2026-07-01) · Jul 2026 · source · release history -
New Outbound SCIM Action template for Event Streams pushes
user.created,user.updated, anduser.deletedevents to any SCIM 2.0-compliant downstream application without custom infrastructure. Automate Downstream Provisioning with Outbound SCIM for Users via Event Streams (2026-07-01) · Jul 2026 · source · release history - Template-driven customization lets practitioners map Auth0 attributes to downstream SCIM schemas and enable opt-in UPSERT (create-on-update) behavior for gradual user trickle-in. Automate Downstream Provisioning with Outbound SCIM for Users via Event Streams (2026-07-01) · Jul 2026 · source · release history
example
-
Enable automated downstream user provisioning to a SCIM 2.0 app without hosting any webhook infrastructure.
In the Auth0 Dashboard, go to Event Streams > Create Stream, select Auth0 Actions as the destination, then apply the Outbound SCIM provisioning template.Automate Downstream Provisioning with Outbound SCIM for Users via Event Streams (2026-07-01) · Jul 2026 · source
Refresh Token Metadata shipped Attach up to 25 custom key-value pairs to refresh tokens at login time via Actions, inspect and update them via the Management API, and use them throughout the token lifecycle for contextual access decisions.
Also counts toward: REST API
release
-
Each delegated setting is independently controllable, allowing platform teams to choose which settings and values are exposed to Organization Admins.
My Organization API and Embeddable UI Components - XAA and third-party app access configuration in Early Acces (2026-09-03) · Sep 2026
· source
· release history
-
New Management API endpoints support retrieving (
GET), updating (PATCH), and revoking (DELETE) refresh tokens with metadata at/api/v2/refresh-tokens/{id}. Refresh Token metadata is now Generally Available (2026-06-22) · Jun 2026 · source · release history - Adds Refresh Token Metadata (GA for Enterprise): attach up to 25 custom key-value pairs to refresh tokens that persist throughout the token lifecycle. Refresh Token metadata is now Generally Available (2026-06-22) · Jun 2026 · source · release history
- New api.refreshToken.setMetadata() method in Post-Login Actions lets you store contextual data (device, region, org) at login time. Refresh Token metadata is now Generally Available (2026-06-22) · Jun 2026 · source · release history
example
-
Inspect a refresh token's stored metadata via the Management API to audit contextual data tied to a specific token.
curl -X GET "https://<your-domain>/api/v2/refresh-tokens/<id>" \ -H "Authorization: Bearer <mgmt_api_token>"Refresh Token metadata is now Generally Available (2026-06-22) · Jun 2026 · source -
Tag refresh tokens with device and region context at login so downstream services can make access decisions without re-querying the IdP.
// Post-Login Action exports.onExecutePostLogin = async (event, api) => { api.refreshToken.setMetadata('deviceName', event.request.user_agent); api.refreshToken.setMetadata('loginRegion',…Refresh Token metadata is now Generally Available (2026-06-22) · Jun 2026 · source -
Update metadata on an existing refresh token — for example, to mark a token as elevated after step-up authentication.
curl -X PATCH "https://<your-domain>/api/v2/refresh-tokens/<id>" \ -H "Authorization: Bearer <mgmt_api_token>" \ -H "Content-Type: application/json" \ -d '{"metadata": {"stepUpCompleted": "true"}}'Refresh Token metadata is now Generally Available (2026-06-22) · Jun 2026 · source
Custom Rate Limit Policies shipped Enables API-based self-service configuration to cap Authentication API and OAuth request consumption for individual or grouped clients, with configurable blocking or non-blocking enforcement modes.
Also counts toward: REST API
release
-
Adds configurable Rate Limit Policy enforcement modes: block requests outright, or trigger non-blocking notifications for safer policy rollout.
changelog · Aug 2026
· source
· release history
- Adds API-based self-service configuration of Custom Rate Limit Policies to cap Authentication API OAuth request consumption per individual client, all third-party apps, or CIMD apps. changelog · Aug 2026 · source · release history
- Supports two enforcement modes per Custom Rate Limit Policy: blocking (reject requests that exceed the limit) or non-blocking (trigger notifications only), allowing safer staged rollouts. Custom Rate Limits available in Early Access (2026-08-17) · Aug 2026 · source · release history
- Adds Custom Rate Limit Policies (Early Access) enabling API-based self-service configuration to cap the number of Authentication API / OAuth requests consumable by individual clients or groups (all third-party apps, or CIMD apps), preventing any single client from exhausting a tenant's rate limit entitlement. Custom Rate Limits available in Early Access (2026-08-17) · Aug 2026 · source · release history
- Enables configuring Rate Limit Policy enforcement modes: block requests or trigger non-blocking notifications Custom Rate Limits available in Early Access (2026-08-17) · Aug 2026 · source · release history
-
Adds
api-based self service configurationof Custom Rate Limit Policies to restrict Authentication API OAuth requests for individual or grouped clients Custom Rate Limits available in Early Access (2026-08-17) · Aug 2026 · source · release history
docs
- August 17, 2026 Custom Rate Limits available in Early Access Custom Rate Limits allow Auth0 Customers to limit the amount of RPS their first-party, third-party, or CIMD apps can consume, so as to mitigate the risk that any one Client can exhaust the customer’s Tenant Rate Limit Entitlement on their tenant’s… changelog · Aug 2026 · source
Token Vault Privileged Worker shipped Allows background or autonomous agents to authenticate via Private Key JWT or mTLS and retrieve a specific user's third-party tokens (Gmail, Drive, Slack, etc.) from Token Vault without requiring an active user session, with per-connection and per-scope credential pinning.
release 7 total
-
Adds Token Vault Privileged Worker (Early Access), allowing background agents to authenticate via Private Key JWT or mTLS and retrieve a specific user's third-party tokens (Gmail, Drive, Slack, etc.) from Token Vault without an active user session, with per-connection and per-scope credential pinning.
changelog · Aug 2026
· source
· release history
- Enables Token Vault Privileged Worker in Early Access to allow autonomous agents to pull third-party tokens (e.g., Gmail, Slack) from Token Vault without a user session Token Vault Privileged Worker is now Early Access! (2026-07-30) · Jul 2026 · source · release history
- Enables pinning each worker credential to specific connections and scopes to limit blast radius of a compromised credential. Token Vault Privileged Worker is now Early Access! (2026-07-30) · Jul 2026 · source · release history
- Allows pinning worker credentials to specific connections and scopes for least-privilege access Token Vault Privileged Worker is now Early Access! (2026-07-30) · Jul 2026 · source · release history
- Supports Private Key JWT and mTLS authentication for trusted worker identities authorizing token exchanges. Token Vault Privileged Worker is now Early Access! (2026-07-30) · Jul 2026 · source · release history
- Supports authentication of trusted worker identities via Private Key JWT or mTLS Token Vault Privileged Worker is now Early Access! (2026-07-30) · Jul 2026 · source · release history
Agent Skills Framework shipped Provides a package of framework-specific quickstart modules and security posture audit capabilities installable into local AI coding environments.
release
-
Adds
auth0 agent skills installsubcommand to install the Auth0 skill into Claude Code, Cursor, or all supported AI assistants in one command.
Agent Mode for the Auth0 CLI (2026-10-21) · Oct 2026
· source
· release history
-
Adds
auth0 docs searchcommand to query Auth0 public documentation directly from the CLI with no login required (returning raw-markdown URLs in agent mode), andauth0 agent skills installcommand to pre-load Auth0 CLI conventions into a coding assistant before first use.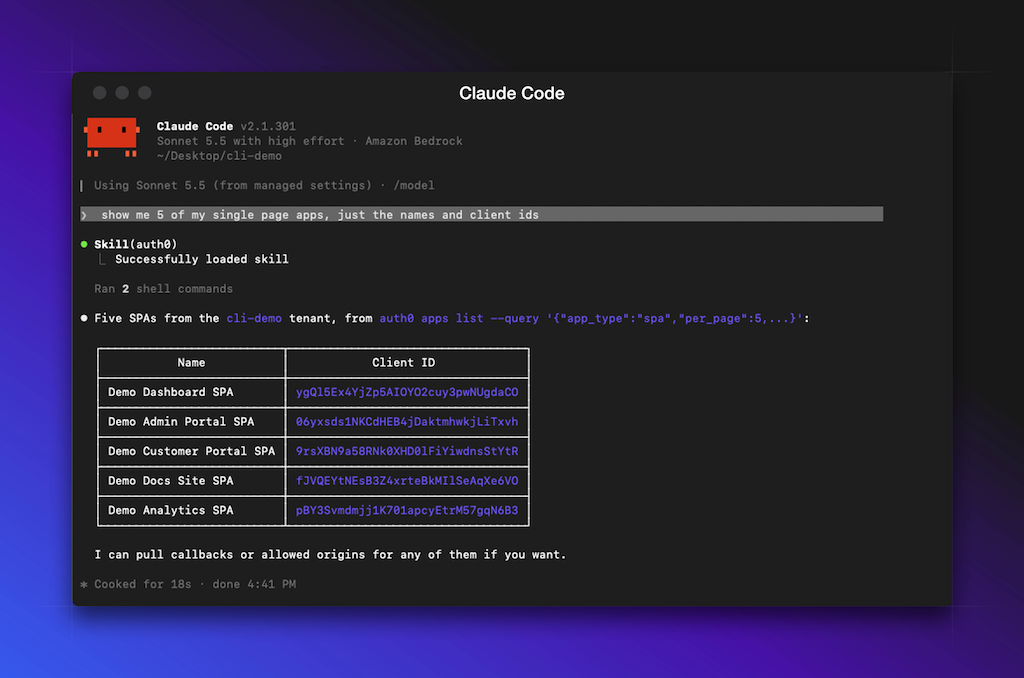 announced · Oct 2026
· source
· release history
-
Adds the
Auth0 HealthCheckskill, which queries a live Auth0 tenant via the Auth0 Management API and Auth0 CheckMate to produce confidence-weighted security posture and capability-fit scores, then generates a prioritized findings report.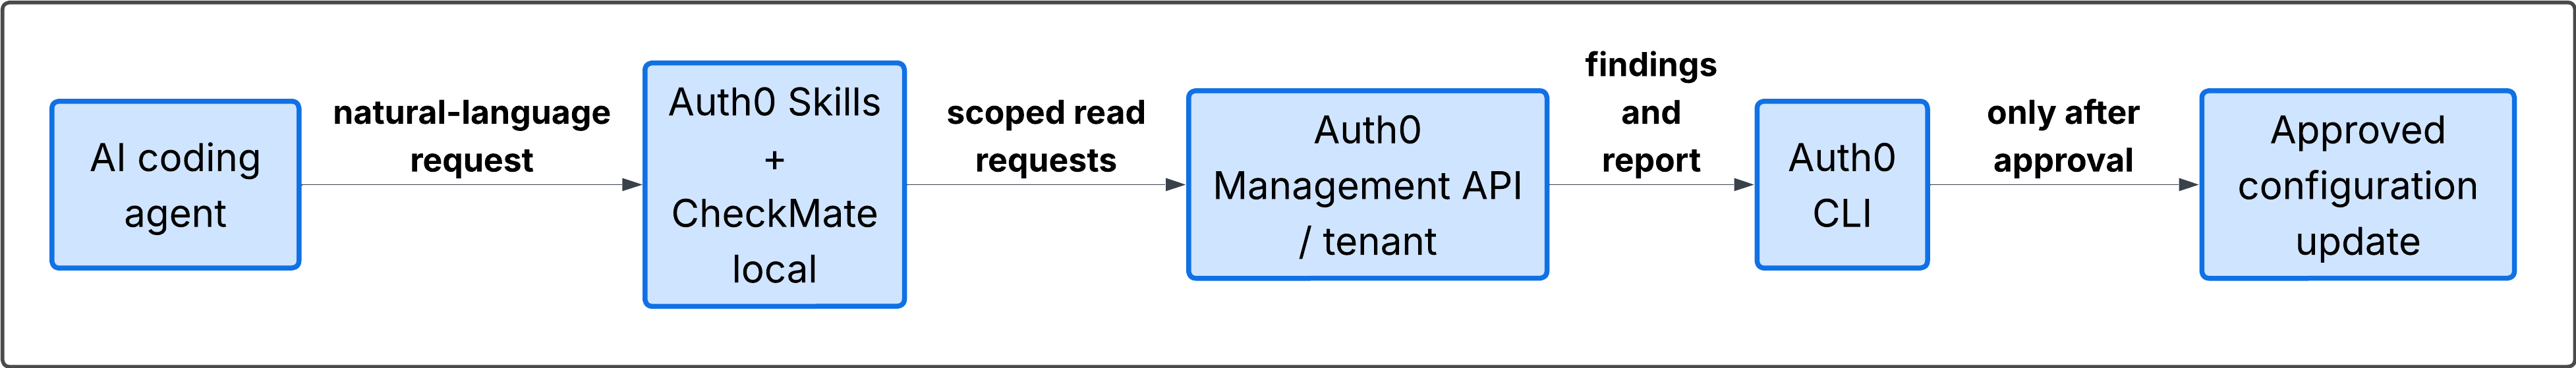 announced · Sep 2026
· source
· release history
- Provides 35+ framework quickstart skill modules that detect the application framework and load relevant SDK guidance for React, Next.js, Node.js, Python, Swift, Flutter, and more. announced · Sep 2026 · source · release history
-
Adds
npx skills add auth0/agent-skillsto install the official Auth0 Agent Skills package into a local terminal or IDE-based AI coding agent.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Sep 2026 · source · release history
example
-
Install Auth0 Agent Skills into your local AI coding environment so your agent can audit live tenant configuration instead of guessing.
npx skills add auth0/agent-skillsannounced · Sep 2026 · source
Auth0 CLI tenant and application management shipped Provides CLI commands to authenticate to a tenant, list configured tenants, stream tenant logs in real time, and list applications in the current tenant.
Also counts toward: Command-line interface
release
-
Adds
auth0 docs searchsubcommand to search Auth0 documentation from the terminal without requiring login.
Agent Mode for the Auth0 CLI (2026-10-21) · Oct 2026
· source
· release history
-
Adds
AUTH0_CLI_AUTH_MODE=envenvironment variable (combined withAUTH0_DOMAINand eitherAUTH0_API_TOKENor client credentials) to run the CLI without touching the OS keychain or writing to disk, for CI runners and sandboxes.
announced · Oct 2026
· source
· release history
example
-
Authenticate the CLI to a tenant.
auth0 login -
List the tenants the CLI is configured for.
auth0 tenants list -
Stream tenant logs in real time.
auth0 logs tail -
List applications in the current tenant.
auth0 apps list
TanStack Start Framework Integration shipped Provides a purpose-built SDK with server and client utilities, hooks, and route guards for integrating authentication into TanStack Start applications.
release
- Adds server-side session helpers getSession(auth0), getAccessToken(auth0), getTokenSet(auth0), and createFetcher(auth0) for use inside TanStack Start server functions. announced · Oct 2026 · source · release history
-
Adds core setup primitives for wiring Auth0 into a TanStack Start app: auth0Server() from
@auth0/auth0-tanstack-start-react/serverfor a server-side Auth0 instance, auth0Middleware() from@auth0/auth0-tanstack-start-react/server/middlewareto register Auth0 and automatically mount/auth/login,/auth/callback,… announced · Oct 2026 · source · release history -
Adds client-side auth state utilities: React hooks
useAuth0,useUser,useOrg,useLogin,useLogout, anduseMfa, and declarative componentsSignedIn,SignedOut,HasOrg,AuthReady, andAuthLoadingfor conditional rendering based on auth state. announced · Oct 2026 · source · release history -
Adds access-control helpers for protecting routes and API handlers:
requireAuthandrequireOrgroute guards for use in a route'sbeforeLoad, plus server middleware helpersrequireAuthMiddleware,withApiAuth,withApiScopes,withApiOrg, and claim-based guardwithApiClaimIncludes. announced · Oct 2026 · source · release history -
Ships a new
@auth0/auth0-tanstack-start-reactSDK purpose-built for TanStack Start, supporting Organizations, MFA, API scope checks, and WebAuthn-based passwordless (passkeys) login. announced · Oct 2026 · source · release history
example
-
Install the SDK and set required environment variables to get Auth0 auth into a TanStack Start project.
npm install @auth0/auth0-tanstack-start-reactannounced · Oct 2026 · source
Organization-scoped roles shipped Defines independent role definitions and permission assignments per Auth0 Organization, manageable via the Management API or Dashboard with opt-in per-org enforcement.
Also counts toward: Role-based access control, REST API, Web management console
release
-
Introduces Organization-Level Roles (Early Access), enabling creation, update, deletion, and assignment of roles scoped to individual organizations via the Management API or Dashboard, including pre-assignment during user invitations.
changelog · Aug 2026
· source
· release history
- Adds organization-scoped roles so each Auth0 Organization can have its own independent role definitions and permission assignments. Organization-Level Roles - Early Access (2026-07-29) · Jul 2026 · source · release history
- Supports per-org, opt-in enforcement so entitlements can be configured and tested before going live, with no risk of disrupting existing login flows. Organization-to-Application Entitlement - Early Access (2026-07-29) · Jul 2026 · source · release history
- Supports creating, updating, and deleting org-scoped roles via the Management API or Dashboard. Organization-Level Roles - Early Access (2026-07-29) · Jul 2026 · source · release history
- Enables assigning org-scoped roles to users and enterprise groups within a specific organization. Organization-Level Roles - Early Access (2026-07-29) · Jul 2026 · source · release history
- Supports pre-assigning an org-scoped role when sending a user invitation to an organization. Organization-Level Roles - Early Access (2026-07-29) · Jul 2026 · source · release history
Client ID Metadata Document (CIMD) Dynamic Registration shipped Allows MCP clients and AI agents to present an HTTPS metadata URL during the OAuth flow for just-in-time discovery and registration, with an optional administrator pre-registration and approval workflow.
release
-
Introduces CIMD (Client ID Metadata Document) with dynamic registration in Early Access, allowing MCP clients and AI agents to connect to a tenant via just-in-time registration using a metadata URL — no pre-registration required.
changelog · Oct 2026
· source
· release history
-
Supports Client ID Metadata Document (CIMD) with dynamic registration (Early Access): MCP clients and AI agents present an HTTPS metadata URL during the OAuth authorization flow and are discovered and registered just-in-time — no administrator pre-registration required.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
CIMD with Dynamic Registration in Early Access (2026-10-22) · Oct 2026
· source
· release history
- Adds CIMD with dynamic registration (Early Access), enabling just-in-time client discovery and registration during an OAuth authorization flow using a client ID metadata URL — without requiring admin pre-registration of every client. announced · Oct 2026 · source · release history
- Adds CIMD with manual pre-registration, letting administrators submit a client metadata URL to Auth0, which retrieves and validates the metadata before creating the client after admin approval.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ announced · Oct 2026 · source · release history
- Supports optional manual pre-registration flow: an administrator submits the client metadata URL, reviews it, and approves the client before creation. CIMD with Dynamic Registration in Early Access (2026-10-22) · Oct 2026 · source · release history
Access Token Scope Customization in Actions shipped Lets Actions add, remove, set, or clear access token scopes at both Credentials Exchange and Post Login stages, with live scope state readable via `event.transaction.target_scopes`, while blocking scope addition for third-party applications to prevent consent bypass.
release
-
Exposes
event.transaction.target_scopesin Actions to read the live target scope list, reflecting every change across chained Actions.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Actions - Access Token Scope Customization - GA (2026-10-09) · Oct 2026
· source
· release history
- api.accessToken.addScope() is no longer available in Actions executed for third-party applications; any existing Action relying on it for third-party apps will need to be migrated to the target scope interfaces. Actions - Access Token Scope Customization - GA (2026-10-09) · Oct 2026 · source · release history
- Extends target scope interfaces (Add, Remove, Set, Clear) to Post Login Actions, in addition to Credentials Exchange Actions. Actions - Access Token Scope Customization - GA (2026-10-09) · Oct 2026 · source · release history
- Adds api.accessToken.addScope() restriction for third-party applications, where it is no longer available to prevent consent bypass. Actions - Access Token Scope Customization - GA (2026-10-09) · Oct 2026 · source · release history
- Promotes Access Token Scope Customization for Actions — including Add, Remove, Set, and Clear scope interfaces — to General Availability for Credentials Exchange Actions. Actions - Access Token Scope Customization - GA (2026-10-09) · Oct 2026 · source · release history
Custom User ID Support shipped Allows assigning custom UUIDs or domain-specific IDs to new database connection users at signup via the Authentication API, Management API, and Universal Login.
Also counts toward: REST API, Scripting API
release
-
Adds api.user.setUserId() method in
onExecutePreUserRegistrationActions to assign custom user IDs (UUIDs, domain-specific, or legacy-compatible formats) to new database-connection users at signup, replacing the need for self-hosted signup pages or bulk import.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
changelog · Sep 2026
· source
· release history
-
Adds api.user.setUserId() method to
pre-user-registrationActions allowing customuser_idassignment at signup
Custom User ID Assignment with Actions — Early Access (2026-09-17) · Sep 2026
· source
· release history
-
Extends custom
user_idsupport to Universal Login sign-up, Authentication API signup endpoint, and Management API Create User endpoint Custom User ID Assignment with Actions — Early Access (2026-09-17) · Sep 2026 · source · release history - Supports custom user IDs across Database connections (including custom databases with automatic migration), Universal Login sign-up, the Authentication API signup endpoint, and the Management API Create User endpoint. Custom User ID Assignment with Actions — Early Access (2026-09-17) · Sep 2026 · source · release history
example
-
Assign a UUID as the custom user ID during database connection signup.
api.user.setUserId(crypto.randomUUID());Custom User ID Assignment with Actions — Early Access (2026-09-17) · Sep 2026 · source
Tenant Network ACL Request Signing and Proxy Verification shipped Enforces RFC 9421 HTTP Message Signatures at the tenant network boundary to verify that incoming requests originate from authorized reverse proxies or gateways, blocking direct tenant bypass, with key-rotation support for zero-downtime signing key updates and audit visibility via `acls_summary` tenant log events.
Also counts toward: Administrative audit log, REST API
release
-
Auth0 Tenant Network ACLs now support RFC 9421 HTTP Message Signatures via the Management API, letting enterprise tenants enforce HMAC-SHA256 request verification at the network boundary to block direct tenant bypass.
HTTP Message Signatures Added to Tenant Network ACLs (2026-10-29) · Oct 2026
· source
· release history
-
Observe key-rotation activity and verification events via
acls_summaryTenant Log events.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ HTTP Message Signatures Added to Tenant Network ACLs (2026-10-29) · Oct 2026 · source · release history - Validate that incoming requests originate only from authorized reverse proxies or gateways, dropping unverified direct traffic. HTTP Message Signatures Added to Tenant Network ACLs (2026-10-29) · Oct 2026 · source · release history
- Rotate signing keys with zero downtime by configuring multiple active signing keys per rule. HTTP Message Signatures Added to Tenant Network ACLs (2026-10-29) · Oct 2026 · source · release history
Experiment Center shipped Enables A/B testing of authentication traffic variants across Universal Login, Forms, Actions, and Page Templates with dedicated exposure and success metrics.
release
-
Adds Experiment Center to A/B test login experiences and review results in metrics dashboards.
Identity Conversion Suite is now in Early Access (2026-10-26) · Oct 2026
· source
· release history
- Introduces the Identity Conversion Suite as a paid add-on for Enterprise plans, combining Anonymous Sessions and Experiment Center. Identity Conversion Suite is now in Early Access (2026-10-26) · Oct 2026 · source · release history
-
Experiment Center captures exposure, success rate, and time-to-auth per variant and segment as dedicated experiment events, enabling data-backed promotion of winning flows.
announced · Sep 2026
· source
· release history
example
-
Create a new Action Module in the Auth0 Dashboard to house shared initialization logic (e.g. an SDK client) that multiple Actions can import instead of each re-running setup code.
In the Auth0 Dashboard, go to Actions > Modules > Create Module, give it a name, add any required secrets and npm dependencies, then write and publish your shared code.
Actions - Modules - GA (2026-09-18) · Sep 2026
· source
Kotlin Multiplatform Mobile SDK shipped Delivers a shared Kotlin Multiplatform SDK for Android and iOS that centralizes authentication, WebAuth, and credential management across mobile apps.
Also counts toward: Client SDKs
release
-
Adds the
auth0umbrella module (com.auth0.kmp:auth0:1.0.0-beta.1) to Maven Central, bundling Web Auth, Authentication API, and credential management into a single KMP artifact usable fromcommonMainshared code, plusauth0-webauthandauth0-credentialsas individual feature modules for lighter-weight… announced · Oct 2026 · source · release history -
Exposes Swift-friendly
async/awaitand exhaustiveswitchvia SKIE (Swift Kotlin Interface Enhancer) so iOS Swift code consumes the same KMP API idiomatically. announced · Oct 2026 · source · release history -
Adds Auth0Account and Auth0 client classes in
com.auth0.kmp, initialised once and sharing a single network transport acrosswebAuth,authentication, and credentials() subsystems. announced · Oct 2026 · source · release history
example
-
Add the Auth0 KMP SDK to a shared module so authentication logic is written once and runs on both Android and iOS.
// shared/build.gradle.kts kotlin { sourceSets { commonMain.dependencies { implementation("com.auth0.kmp:auth0:1.0.0-beta.1") } } }announced · Oct 2026 · source
Auth0 Agent Gateway Policy Enforcement shipped Provides a centralized layer to evaluate tool-call authorization in real time using agent, user, and organization context, including agent kill switch controls.
Also counts toward: Multi-tenant management
release
-
New Auth0 Agent Gateway beta provides a centralized policy-enforcement layer that evaluates tool-call authorization in real time using agent, user, and organization context before any external tool is invoked.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
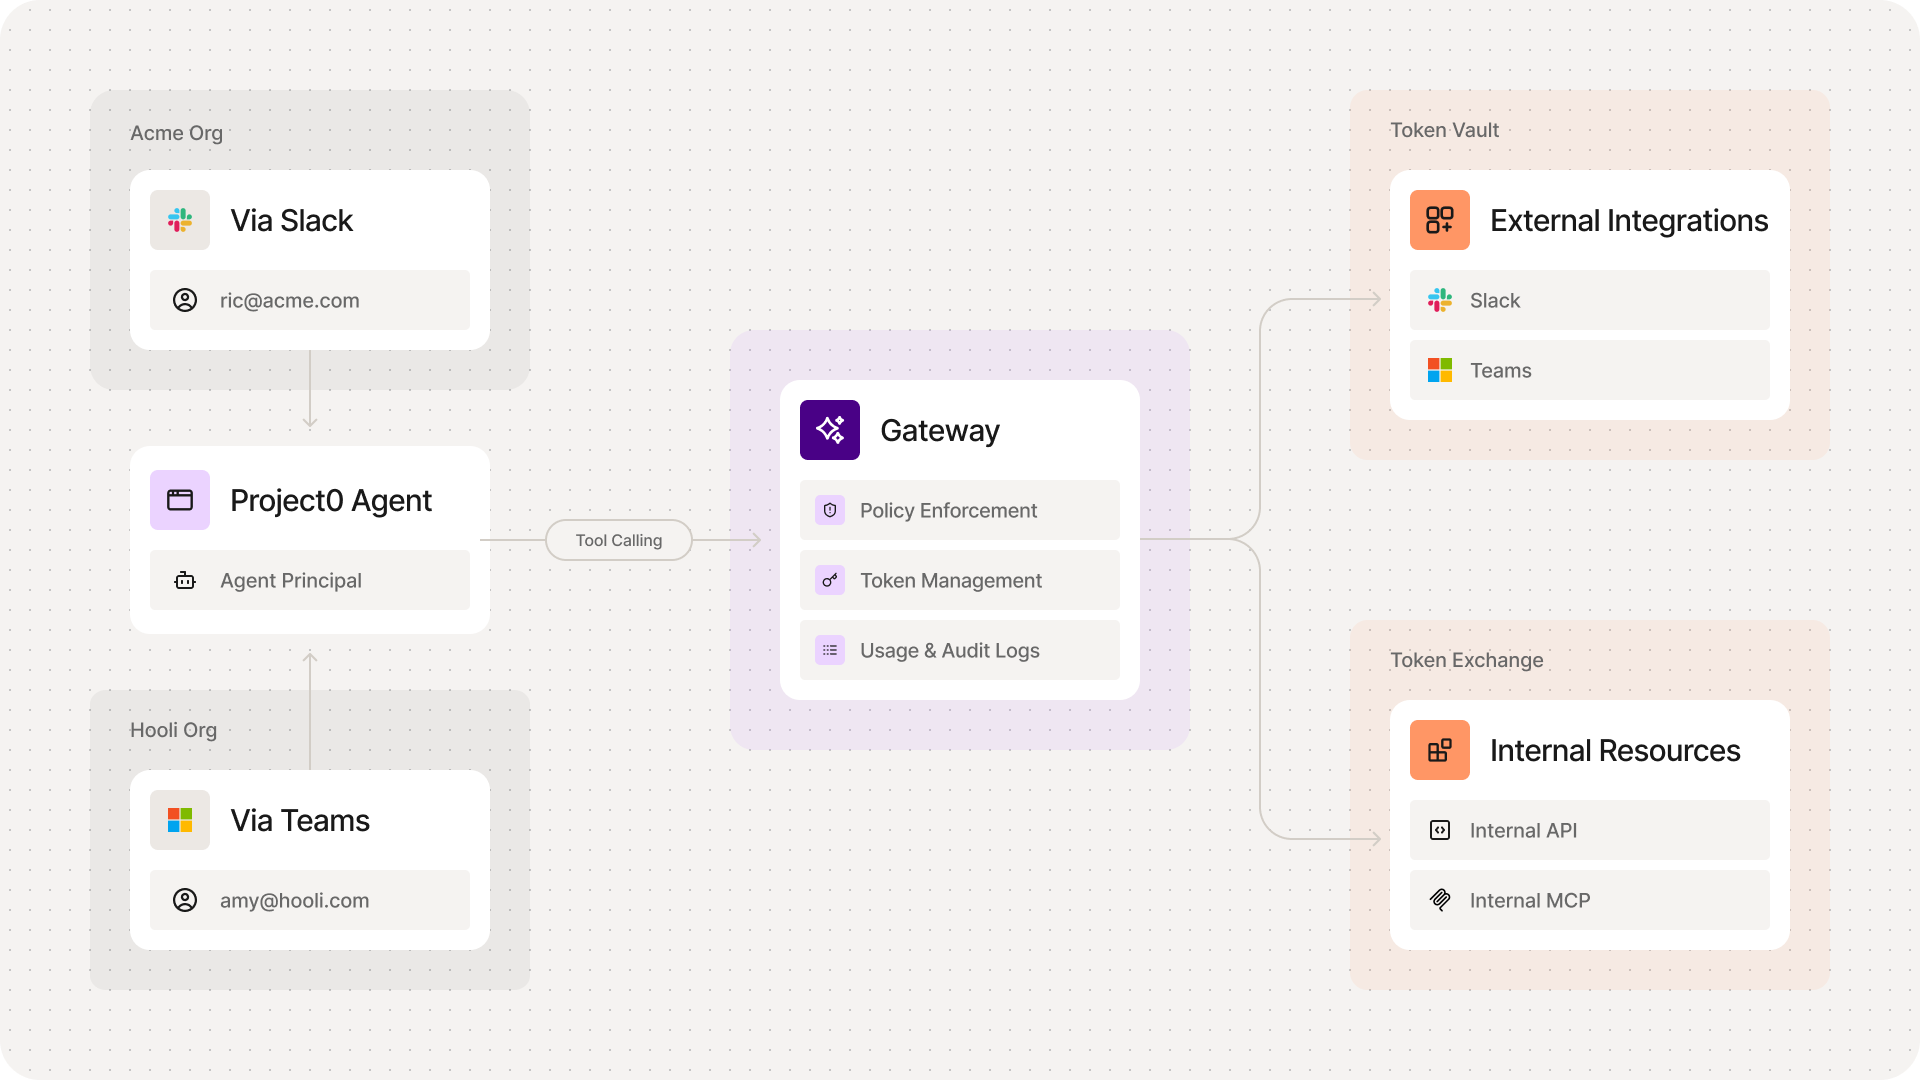 announced · Sep 2026
· source
· release history
- Supports organization-aware, multi-tenant routing that isolates tool access and connected credentials (e.g. Slack, Microsoft Teams) per customer tenant, preventing cross-tenant data exposure. announced · Sep 2026 · source · release history
- Integrates with Auth0 Token Vault and on-behalf-of token exchange to broker short-lived, user-scoped tokens for internal and external APIs — keeping raw credentials out of LLM prompts, context windows, and logs. announced · Sep 2026 · source · release history
- Provides an agent kill switch — centralized administrative controls to disable an agent or restrict its access to downstream services and tools across a tenant or deployment. announced · Sep 2026 · source · release history
Custom Prompts for Social and Enterprise Connections shipped Extends Universal Login custom signup/login fields and consent checkboxes to Social and Enterprise connections, so users cannot bypass those prompts when authenticating via a social button or enterprise IdP.
release
-
Custom Prompts (custom signup/login fields and consent checkboxes configured in Universal Login) now capture data on Social and Enterprise connections in addition to database and passwordless connections, with no configuration changes required — reviewable under Branding → Universal Login → Enhance screens with…
changelog · Aug 2026
· source
· release history
- Custom Prompt fields now capture data for social and enterprise identity provider logins/signup Custom Prompts now capture the same fields on Social and Enterprise connections (2026-08-10) · Aug 2026 · source · release history
- Custom signup/login fields and consent checkboxes configured in Universal Login now apply to Social and Enterprise connections, closing the gap where users could bypass those prompts entirely when signing in via a social button or enterprise identity provider. Custom Prompts now capture the same fields on Social and Enterprise connections (2026-08-10) · Aug 2026 · source · release history
- No configuration changes required — existing Custom Prompts setups automatically extend to all connection types; review or update via Dashboard under Branding → Universal Login → Enhance screens with partials, or via the Management API. Custom Prompts now capture the same fields on Social and Enterprise connections (2026-08-10) · Aug 2026 · source · release history
Organization member search and filtering shipped Search Organization members in real time by name, email, or ID and filter by blocked status directly from the Auth0 Dashboard.
Also counts toward: Web management console
release
-
Adds real-time Dashboard Search for Organization Members (Public Beta), supporting search by name, email, ID, and filtering by blocked status.
changelog · Aug 2026
· source
· release history
- Filter Organization members by blocked status from the Dashboard member search interface. Dashboard Search for Organization members now in Beta! (2026-07-29) · Jul 2026 · source · release history
- Search Organization members in real time by name, email, or ID directly from the Auth0 Dashboard — no more paginating through full member lists. Dashboard Search for Organization members now in Beta! (2026-07-29) · Jul 2026 · source · release history
example
-
Quickly locate a specific organization member without scrolling through paginated lists.
In the Dashboard, go to Organizations > [your organization] > Members, then use the search bar to enter a name, email address, or user ID.Dashboard Search for Organization members now in Beta! (2026-07-29) · Jul 2026 · source
FGA Permissions Index shipped Precomputes access relations for Fine-Grained Authorization and streams results to a customer database to enable constant-time permission lookups.
Also counts toward: Web management console
release
-
Graduates the FGA Permissions Index from Developer Preview to Early Access, with self-service build/monitor/manage inside the FGA Dashboard; Enterprise subscriptions include one index with up to 10 million expansions, with a paid add-on scaling to 10 indexes and higher expansion limits.
changelog · Oct 2026
· source
· release history
-
Introduces FGA Permissions Index (Early Access), which precomputes every access implied by chosen relations (e.g.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
can_view) on an object type and streams the results directly into the customer's own database, enabling a simple SQL JOIN instead of runtime graph traversal for… announced · Sep 2026 · source · release history - Supports indexing high-cardinality relations on an object type so that permission lookups on indexed relations become constant-time, while non-indexed relations continue to be evaluated by FGA in real time. announced · Sep 2026 · source · release history
Universal Login Phone & Identifier UI Customization shipped Allows tenant administrators to customize the Universal Login UI with improved phone entry fields, country filtering, and identifier presentation options.
Also counts toward: REST API
release
-
Adds an updated phone entry UI for Universal Login with country selection, regional formatting, numeric keyboard, and phone number suggestions on supported devices.
Universal Login identifier and phone country controls in Early Access (2026-10-16) · Oct 2026
· source
· release history
-
Adds tenant-level include/exclude lists for supported phone countries, configurable via the
PATCH /api/v2/tenants/settingsendpoint.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Universal Login identifier and phone country controls in Early Access (2026-10-16) · Oct 2026 · source · release history -
Adds identifier presentation controls (type-specific Continue with buttons vs. unified field) configurable via the
PATCH /api/v2/branding/themeendpoint. Universal Login identifier and phone country controls in Early Access (2026-10-16) · Oct 2026 · source · release history
Customizable MFA OTP Lifetimes shipped Allows administrators to configure the validity window for one-time passcodes used in SMS and email MFA flows.
release
-
Configurable OTP lifetime for SMS MFA (30 seconds to 1 hour) and email MFA (5 minutes to 1 hour).
Advanced MFA Configurations are now Generally Available (2026-09-01) · Sep 2026
· source
· release history
- Allows configuring OTP validity lifetime for SMS MFA between 30 seconds and 1 hour. Advanced MFA Configurations are now Generally Available (2026-09-01) · Sep 2026 · source · release history
- Allows configuring OTP validity lifetime for Email MFA between 5 minutes and 1 hour. Advanced MFA Configurations are now Generally Available (2026-09-01) · Sep 2026 · source · release history
Organization-to-Application Entitlement shipped Natively enforces which applications members of an organization can access, automatically denying unauthorized login attempts without requiring custom Actions, metadata checks, or logic.
release
-
Org-aware token resolution: in multi-org tenants, requests are scoped by
org_idand rejected if the enterprise connection or target resource app is not enabled for that organization, or if the org context is ambiguous across multiple identities.
Cross-App Access Requesting App now in Early Access (2026-08-31) · Aug 2026
· source
· release history
-
Adds Organization-to-Application Entitlement (Early Access), allowing per-org control over which applications organization members can access — enforced natively in Auth0 without custom Actions or metadata logic, opt-in and disabled by default.
changelog · Aug 2026
· source
· release history
- Adds Organization-to-Application Entitlement (Early Access): natively enforce which applications members of an organization can access, with automatic denial on unauthorized login attempts — no Actions, metadata checks, or custom logic required. Organization-to-Application Entitlement - Early Access (2026-07-29) · Jul 2026 · source · release history
Configurable API Request Retry Policies shipped Enables developers to define fixed or exponential backoff retry policies for outgoing API requests.
release
-
An initial buffer of immediate retry attempts accommodates typos or delivery delays before progressive wait times take effect.
Multi-Factor Authentication: Exponential Backoff for Phone MFA SMS Delivery (2026-10-30) · Oct 2026
· source
· release history
-
Adds configurable retry behaviour via
RetryPolicyinRequestOptions, supporting fixed or exponential backoff on API requests. announced · Oct 2026 · source · release history
Brute-Force Protection Unblock Behavior shipped Adds a configurable Unblock Behavior setting to Brute-Force Protection, with Automatic (default) and Manual modes — Manual mode prevents email security scanners from consuming recovery links before the user opens them.
release
-
Adds an Unblock Behavior setting to Brute-Force Protection (
Auth0 Dashboard > Security > Attack Protection > Brute-Force Protection), with Automatic (default) and Manual modes — Manual mode prevents email security scanners from consuming recovery links before the user opens them.
changelog · Oct 2026
· source
· release history
example
-
Configure Manual unblock mode so email security scanners cannot accidentally consume recovery links and unblock accounts prematurely.
Auth0 Dashboard > Security > Attack Protection > Brute-Force Protection > Unblock Behavior > select 'Manual' > Savechangelog · Oct 2026 · source
Application Profiles shipped Centralises management of third-party applications used by AI agents and enables B2B behaviour configuration for DCIMD applications, controlling whether they serve individuals, organisations, or both, along with login experience settings.
release
-
Adds B2B behaviour configuration for DCIMD applications via Application Profiles, controlling whether applications serve individuals, organizations, or both, along with login experience settings.
Application Profiles are available in Early Access (2026-10-22) · Oct 2026
· source
· release history
- Enables centralized management of third-party applications created and used by AI agents through Application Profiles. Application Profiles are available in Early Access (2026-10-22) · Oct 2026 · source · release history
Direct Authentication API & Passkey Support shipped Enables passwordless passkey enrollment and direct Authentication API calls from native apps, with optional browser-based Universal Login flows.
Also counts toward: Client SDKs
release
-
Adds auth0.webAuth.login(LoginOptions(...)) and auth0.webAuth.logout() suspend functions that open Universal Login via Custom Tabs (Android) or
ASWebAuthenticationSession(iOS) and return a sealed Result type. announced · Oct 2026 · source · release history -
Adds the
auth0.authenticationclient for direct Authentication API access (sign-in with username/password, user creation, and profile fetch without a browser redirect), including WebAuthn passkey enrolment and sign-in through the same client. announced · Oct 2026 · source · release history
Secure Local Credentials Management shipped Provides a platform-native credentials manager that stores tokens securely and automatically renews expired access tokens without user interaction.
release
-
Adds the auth0.credentials() Credentials Manager backed by Keystore-encrypted DataStore on Android and Keychain on iOS, with
saveCredentials,getCredentials,hasValidCredentials, andclearCredentialsmethods that auto-renew expired access tokens via refresh token, plus a Storage interface for supplying a… announced · Oct 2026 · source · release history
example
-
Silently renew an expired access token and retrieve a fresh credential without prompting the user, using the built-in Credentials Manager.
import com.auth0.kmp.core.result.Result val manager = auth0.credentials() when (val result = manager.getCredentials()) { is Result.Success -> { val accessToken = result.data.accessToken // attach…announced · Oct 2026 · source
Agents as Principal shipped Gives each AI agent a unique first-class identity with its own credentials and audit trail, distinct from human users and shared clients, with the full delegation chain encoded in tokens.
release
-
Introduces Agents as Principal (Early Access), giving AI agents a unique first-class identity with their own credentials, audit trail, and delegation chain encoding in tokens — separate from human users and shared clients.
changelog · Aug 2026
· source
· release history
- Introduces Agents as Principal: every AI agent gets a unique identity distinct from human users and shared clients, with its own credentials and audit trail. Agents as Principal now in Early Access! (2026-07-30) · Jul 2026 · source · release history
Role search in Dashboard shipped Real-time search for Roles by ID or name in the Auth0 Dashboard, replacing paginated list scrolling.
release
- Adds real-time search for Roles by ID and name in the Auth0 Dashboard, replacing paginated list scrolling (Public Beta, rolling out to Public Cloud tenants). Dashboard Search for Roles Now in Beta (2026-07-14) · Jul 2026 · source · release history
example
-
Quickly locate a specific Role without scrolling through paginated lists — useful when managing large numbers of roles.
In the Auth0 Dashboard, go to User Management > Roles and type a Role name or ID into the search bar to filter results in real time.Dashboard Search for Roles Now in Beta (2026-07-14) · Jul 2026 · source
Google One Tap authentication shipped Lets users authenticate instantly via a Google One Tap overlay in the Universal Login prompt, without manual forms or page redirects.
release
- Adds Google One Tap support to the Universal Login prompt (Early Access), letting users authenticate instantly via a non-intrusive identity overlay without manual forms or page redirects. Google One Tap Support for Universal Login EA (2026-07-09) · Jul 2026 · source · release history
example
-
Enable Google One Tap on your web app via the Auth0 Google Social Connection settings — navigate to the configuration documented in the Auth0 Google Social Connection docs.
In the Auth0 Dashboard, go to Authentication > Social > Google > Settings and enable the Google One Tap option for your Universal Login prompt.Google One Tap Support for Universal Login EA (2026-07-09) · Jul 2026 · source
User Profile Metadata management documented Stores and manages user-level and application-level metadata on Auth0 user profiles — data not originating from an identity provider — via the Dashboard, Management API, or post-login Actions.
Also counts toward: REST API, Web management console
docs
- User profiles have two kinds of metadata (user and application) that let you store information that does not originate from an identity provider. How to Manage User Profile Metadata Access and set user and app metadata in user profiles using the Auth0 Dashboard, Management API, or a post-login Action. seen Oct 2026 · source
- Concepts Understand how user profiles work in Auth0. User profiles have three types of metadata (user, application, and client) that let you store information that does not originate from an identity provider. Normalized User Profile Attributes Understand how Auth0 normalizes common attributes in the user profile. seen Sep 2026 · source
SMS Fraud Throttling Audit Logging shipped Records throttled SMS send attempts as `limit_phone` tenant log events, including remaining cooldown durations, to provide audit visibility into fraud-throttling activity.
Also counts toward: Administrative audit log
release
-
Auth0 now logs throttled SMS send attempts as
limit_phonetenant log events, including remaining cooldown durations, for audit visibility into fraud-throttling activity.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Multi-Factor Authentication: Exponential Backoff for Phone MFA SMS Delivery (2026-10-30) · Oct 2026
· source
· release history
Audience-Scoped Token Refresh shipped Permits exchanging a single refresh token for multiple audience-specific access tokens, allowing one session to interact with several APIs.
release
- Adds getApiCredentials(...) to exchange a refresh token for audience-scoped tokens, enabling a single login session to call multiple APIs. announced · Oct 2026 · source · release history
Native-to-Web Session Continuity shipped Facilitates seamless cross-platform SSO by allowing a native mobile session to transfer its context to a web browser using session-transfer tokens.
release
- Adds native-to-web SSO via session-transfer tokens so a native session can continue in the browser. announced · Oct 2026 · source · release history
Agent Tool Call Audit Logging shipped Records every agent tool invocation in tenant logs with optional streaming export to SIEM platforms for compliance and monitoring.
Also counts toward: Administrative audit log, SIEM forwarding
release
-
Logs every agent tool call to tenant logs with optional streaming export to SIEM services for enterprise auditability.
announced · Sep 2026
· source
· release history
Global Search shipped Provides a unified Command Palette search across Applications, APIs, Organizations, and Users by name, ID, email, or identifier.
release
- Adds Global Search via the Command Palette (Cmd+K) to search Applications, APIs, Organizations, and Users by name, ID, email, or identifier Global Search in Cmd+K is now in Beta (2026-07-31) · Jul 2026 · source · release history
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
15 commands for Auth0, each with where it came from. This tool has no source analysis yet, so there is no option reference and no captured run beside them.
No command matches.
Screenshots
From the release notes, newest first. Click one to see it full size.Media
Videos from the release notes, newest first. They play right here.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for Auth0, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail Auth0 puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Commercials
pricing & packaging history · Okta (Auth0) vendor page52 readings of Okta (Auth0)'s pricing page since Sep 2021, with 19 changes to what its plans include — each one dated, compared with the reading before it, and explained for someone buying the tool.
Pricing and packaging history is included with Researcher and Business. See how every vendor we track sells, and how that has changed over time, using data we don't publish anywhere else.
See plans → Already subscribed? Sign in →Plans by offering
Each offering on the pricing page links to its own page of plans, read at its latest capture.
Plan relaunches
Plans, prices and descriptions are quoted from the vendor's own pricing page as we read it on each date. A plan missing from a later reading is shown as no longer listed on the page — a statement about the page, not the product. Readings that failed to show any plans are left out rather than read as a change.
Website history
auth0.com, every changeOkta (Auth0)'s home, pricing and product pages and 37 more pages as they looked each month from September 2021 to October 2026: 74 renders, 14 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Coverage
Missing something? Tell us
What Auth0 connects to, runs on and detects, read from its release notes and docs. So far: 2 new integrations, 1 updated detection.
3 changes, tracked since Sep 28, 2026.
-
Oct 222026
new Terraform Auth0 Modules — b2b-saas-starter
With auth0/modules/auth0//modules/b2b-saas-starter, Terraform Registry
Terraform Auth0 Modules package that foundation into ready-made modules built on top of the provider. The first module, b2b-saas-starter , is now available on the Terraform Registry .
-
Oct 202026
updated Bot Detection Model Update — expanded IPv6 signal analysis
With fast-rotating IPv6 address ranges, distributed botnets
Expanded signal analysis across fast-rotating IPv6 address ranges commonly exploited by distributed botnets to detect and mitigate automated attacks earlier in the authentication flow.
-
Sep 282026
new Auth0 plugin for ChatGPT
With ChatGPT Codex
Starting today, the Auth0 plugin connects ChatGPT Codex to your actual Auth0 tenant.
Coding agents 1
Chat & assistant apps 1
Identity & access 1
Cloud platforms & services 1
Nothing first seen in this window. That doesn't mean Auth0 shipped nothing, only that we found no record of it.
How we count
Read from 18 of 81 release notes and docs updates we hold for Auth0. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through Auth0's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
81 entries
No entries match these filters.
- October 202620
- September 202624
- August 202614
- July 202620
- June 20263
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →