GitHub
BYOK and enterprise custom models in the Copilot usage API (2026-11-04) commercialThe section your link pointed to isn't on GitHub's page any more, so we've brought you to the top.
GitHub is a web-based platform for version control and collaborative software development using Git repositories.
curl -H 'Authorization: Bearer <token>' \
  'https://api.github.com/enterprises/<enterprise>/copilot/usage?days=1' \
  | jq '[.[] | select(.used_local_byok == true) | {login, used_local_byok, totals_by_local_byok}]'
curl -H 'Authorization: Bearer <token>' \
  'https://api.github.com/enterprises/<enterprise>/copilot/usage?days=28' \
  | jq '[.[] | .totals_by_client[] | .totals_by_model[] | select(.is_custom_enterprise_model == true)]'
version: 2
updates:
  - package-ecosystem: "apm"
    directory: "/"
    schedule:
      interval: "weekly"
curl -s https://api.github.com/meta | jq '.hooks'
copilot plugin install github-security@awesome-copilot
/security-review
/research How do these components retry failed charges, and where could retries overlap?
/research Identify all repositories still calling the old payment API and list the changes each service needs to migrate.
code agent host --github-environment
# 1. In VS Code Settings, enable chat.agentHost.computerUse.enabled and restart VS Code
# 2. In a Copilot session panel, run:
/computer on
chat.copilot.localModel.enabled: true
gh aw forecast
gh aw add-wizard
/permissions
# Then select: assisted
curl -H 'Authorization: Bearer <token>' -H 'Accept: application/vnd.github+json' 'https://api.github.com/orgs/<org>/copilot/metrics?report=1-day' | jq '.totals_by_client[] | {client: .client, requests: .request_count, sessions: .session_count}'
curl -H 'Authorization: Bearer <token>' -H 'Accept: application/vnd.github+json' 'https://api.github.com/enterprises/<enterprise>/copilot/metrics?report=28-day' | jq '.day_totals[] | {date: .date, by_client: [.totals_by_client[] | {client: .client, models: [.totals_by_model[] | {model: .model, mode: .model_selection_mode, requests: .request_count}]}]}'
curl -H "Authorization: Bearer <token>" -H "Accept: application/vnd.github+json" "https://api.github.com/enterprises/<enterprise>/secret-scanning/public-monitoring-alerts?state=open"
gh auth login --expiring
gh config set expiring_credentials enabled
gh auth setup-git
curl -H 'Authorization: Bearer <token>' \
  'https://api.github.com/repos/<owner>/<repo>/dependabot/alerts/<alert_number>' \
  | jq '.dependency.version_requirement'
curl -H 'Authorization: Bearer <token>' \
  'https://api.github.com/repos/<owner>/<repo>/dependabot/alerts?state=open&per_page=100' \
  | jq '.[] | {package: .dependency.package.name, version_requirement: .dependency.version_requirement, severity: .security_advisory.severity}'
curl -L \
  -H "Authorization: Bearer <token>" \
  -H "Accept: application/vnd.github+json" \
  https://api.github.com/enterprises/{enterprise}/copilot/model-policies
curl -L \
  -X PATCH \
  -H "Authorization: Bearer <token>" \
  -H "Accept: application/vnd.github+json" \
  -H "Content-Type: application/json" \
  https://api.github.com/enterprises/{enterprise}/copilot/model-policies \
  -d '{"mode": "organization"}'
curl -X PATCH \
  -H 'Authorization: Bearer <token>' \
  -H 'Accept: application/vnd.github+json' \
  https://api.github.com/repos/<owner>/<repo>/code-scanning/alerts/<alert_number> \
  -d '{"assignees": ["copilot-swe-agent[bot]"]}'
curl -X POST https://api.github.com/orgs/{org}/repos \
  -H 'Authorization: Bearer <installation_token>' \
  -H 'Accept: application/vnd.github+json' \
  -d '{"name": "my-new-repo", "private": true}'
curl -X PUT https://api.github.com/orgs/{org}/installations/{installation_id}/repositories/{repository_id} \
  -H 'Authorization: Bearer <installation_token>' \
  -H 'Accept: application/vnd.github+json'
curl -X GET https://api.github.com/apps/{app_slug} \
  -H 'Authorization: Bearer <jwt_or_installation_token>' \
  -H 'Accept: application/vnd.github+json'
forceRemoteSettingsRefresh: true
curl -i -H 'Authorization: Bearer <token>' \
  https://api.github.com/repos/<owner>/<repo>/dependabot/alerts/<alert_number>
# HTTP/2 410 Gone  →  alert was withdrawn (advisory no longer valid)
# HTTP/2 404 Not Found  →  alert number never existed
telemetry:
  capture:
    identity: true
    toolArguments: true
    prompts: false
    responses: false
    toolOutput: false
    policyDetail: false
/model
codeql query compile --dump-dil --dil-constants my-query.ql
!github
/security-review
/security-review
/model
/model
npm stage publish
npm stage publish
curl -X POST \
  -H 'Authorization: Bearer <token>' \
  -H 'Accept: application/vnd.github+json' \
  https://api.github.com/repos/<owner>/<repo>/security-advisories/<ghsa_id>/comments \
  -d '{"body": "Triage complete: exploitability confirmed on v2.3.1. Patch queued for next release."}'
curl -H 'Authorization: Bearer <token>' \
  -H 'Accept: application/vnd.github+json' \
  'https://api.github.com/repos/<owner>/<repo>/security-advisories' \
  | jq '[.[] | select(.comments_count > 0) | {ghsa_id, summary, comments_count}]'
curl -H 'Authorization: Bearer <token>' \
  -H 'Accept: application/vnd.github+json' \
  'https://api.github.com/repos/<owner>/<repo>/security-advisories/<ghsa_id>/comments?since=2026-01-01T00:00:00Z'
curl -X POST \
  -H 'Authorization: Bearer <token>' \
  -H 'Accept: application/vnd.github+json' \
  https://api.github.com/repos/<owner>/<repo>/security-advisories/<ghsa_id>/comments \
  -d '{"body": "Triage complete: exploitability confirmed on v2.3.1. Patch queued for next release."}'
curl -H 'Authorization: Bearer <token>' \
  -H 'Accept: application/vnd.github+json' \
  'https://api.github.com/repos/<owner>/<repo>/security-advisories' \
  | jq '[.[] | select(.comments_count > 0) | {ghsa_id, summary, comments_count}]'
curl -H 'Authorization: Bearer <token>' \
  -H 'Accept: application/vnd.github+json' \
  'https://api.github.com/repos/<owner>/<repo>/security-advisories/<ghsa_id>/comments?since=2026-01-01T00:00:00Z'
# .github/VULNERABILITY_REPORT.yml in your org's .github repo
name: Vulnerability Report
description: Report a security vulnerability
body:
  - type: textarea
    id: summary
    attributes:
      label: Summary
    validations:
      required: true
      min_length: 50
  - type: textarea
    id: details
    attributes:
      label: Details
    validations:
      required: true
      min_length: 100
  - type: textarea
    id: poc
    attributes:
      label: Proof of Concept
    validations:
      required: true
      min_length: 150
  - type: textarea
    id: impact
    attributes:
      label: Impact
    validations:
      required: true
# .github/VULNERABILITY_REPORT.yml in your org's .github repo
name: Vulnerability Report
description: Report a security vulnerability
body:
  - type: textarea
    id: summary
    attributes:
      label: Summary
    validations:
      required: true
      min_length: 50
  - type: textarea
    id: details
    attributes:
      label: Details
    validations:
      required: true
      min_length: 100
  - type: textarea
    id: poc
    attributes:
      label: Proof of Concept
    validations:
      required: true
      min_length: 150
  - type: textarea
    id: impact
    attributes:
      label: Impact
    validations:
      required: true
/computer on
/computer show
/computer off
/computer on
/computer show
/computer off
gh copilot --experimental
/experimental on
What dynamic workflows are available?
gh copilot --experimental
/experimental on
What dynamic workflows are available?
chat.copilot.hydraFusion.enabled
/sandbox on
{
  "telemetry": {
    "endpoint": "https://otel-collector.example.com"
  }
}
/lsp logs
ssh-keygen -t ed25519 -C "your_email@example.com"
# or, if RSA is required for compatibility:
ssh-keygen -t rsa -b 3072 -C "your_email@example.com"
npm stage publish
jobs:
  build:
    runs-on: ubuntu-26.04-arm
    steps:
      - uses: actions/checkout@v4
      - run: make test
jobs:
  build:
    runs-on: ubuntu-24.04
    steps:
      - uses: actions/checkout@v4
      - run: make test
curl -X PATCH \
  -H 'Authorization: Bearer <token>' \
  -H 'Accept: application/vnd.github+json' \
  -d '{"enabled": true}' \
  https://api.github.com/repos/{owner}/{repo}/code-scanning/ai-scan
curl -X GET \
  -H 'Authorization: Bearer <token>' \
  -H 'Accept: application/vnd.github+json' \
  https://api.github.com/orgs/{org}/code-scanning/ai-scan
curl -X PATCH \
  -H 'Authorization: Bearer <token>' \
  -H 'Accept: application/vnd.github+json' \
  -d '{"enabled": true}' \
  https://api.github.com/repos/{owner}/{repo}/code-scanning/ai-scan
curl -X GET \
  -H 'Authorization: Bearer <token>' \
  -H 'Accept: application/vnd.github+json' \
  https://api.github.com/orgs/{org}/code-scanning/ai-scan
on:
  pull_request:

permissions:
  contents: read

cache-mode: read

jobs:
  build:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
      - uses: actions/cache@v4
        with:
          path: ~/.npm
          key: ${{ runner.os }}-node-${{ hashFiles('**/package-lock.json') }}
      - run: npm ci
on:
  push:
    branches: [main]

jobs:
  seed-cache:
    runs-on: ubuntu-latest
    cache-mode: write-only
    steps:
      - uses: actions/checkout@v4
      - uses: actions/cache@v4
        with:
          path: dist/
          key: ${{ runner.os }}-dist-${{ github.sha }}
      - run: npm run build
on:
  pull_request:

permissions:
  contents: read

cache-mode: read

jobs:
  build:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
      - uses: actions/cache@v4
        with:
          path: ~/.npm
          key: ${{ runner.os }}-node-${{ hashFiles('**/package-lock.json') }}
      - run: npm ci
on:
  push:
    branches: [main]

jobs:
  seed-cache:
    runs-on: ubuntu-latest
    cache-mode: write-only
    steps:
      - uses: actions/checkout@v4
      - uses: actions/cache@v4
        with:
          path: dist/
          key: ${{ runner.os }}-dist-${{ github.sha }}
      - run: npm run build
/feedback
/feedback
curl -H "Authorization: Bearer <token>" \
  -H "Accept: application/vnd.github+json" \
  https://api.github.com/actions/runners/deprecations/2.315.0
permissions:
  vulnerability-alerts: read

jobs:
  audit-alerts:
    runs-on: ubuntu-latest
    steps:
      - name: List Dependabot alerts
        run: gh api repos/${{ github.repository }}/dependabot/alerts
jobs:
  called-job:
    runs-on: ubuntu-latest
    steps:
      - name: Print reusable workflow identity
        run: |
          echo "Workflow ref: ${{ job.workflow_ref }}"
          echo "Workflow SHA: ${{ job.workflow_sha }}"
          echo "Repository:   ${{ job.workflow_repository }}"
          echo "File path:    ${{ job.workflow_file_path }}"
curl -H "Authorization: Bearer <token>" \
  -H "Accept: application/vnd.github+json" \
  https://api.github.com/actions/runners/deprecations/2.315.0
permissions:
  vulnerability-alerts: read

jobs:
  audit-alerts:
    runs-on: ubuntu-latest
    steps:
      - name: List Dependabot alerts
        run: gh api repos/${{ github.repository }}/dependabot/alerts
jobs:
  called-job:
    runs-on: ubuntu-latest
    steps:
      - name: Print reusable workflow identity
        run: |
          echo "Workflow ref: ${{ job.workflow_ref }}"
          echo "Workflow SHA: ${{ job.workflow_sha }}"
          echo "Repository:   ${{ job.workflow_repository }}"
          echo "File path:    ${{ job.workflow_file_path }}"
gh issue create --title 'Login button misaligned on mobile' --body 'See screenshot for the rendering issue.' --attach './screenshot.png#Login button misaligned'
gh pr create --title 'Smooth out modal animation' --body 'Before and after recordings attached.' --attach './before.mp4#Before' --attach './after.mp4#After'
gh issue comment 42 --body 'Reproduced on v2.99.0 — error visible here:' --attach './error.png#Error on screen'
/rubber-duck
jobs:
  build:
    runs-on: windows-11-vs2026-arm
    steps:
      - uses: actions/checkout@v4
      - name: Build
        run: msbuild MyProject.sln
allowedMcpServers:
  - https://mcp.example.com/approved
deniedMcpServers:
  - https://mcp.untrusted.io
permissions:
  disableBypassPermissionsMode: disable
GET https://github.com/login/oauth/authorize?client_id=<client_id>&scope=repo%20offline_access&redirect_uri=https://app.example.com/callback
/rewind
Summary
GitHub is a commercial software development platform run as a hosted service (with a self-hosted Enterprise Server option) that combines git repository hosting with tools for building, securing, and shipping code. Its security features — secret scanningsecret scanningChecking files, code or other data for exposed credentials such as passwords, API keys and tokens. Findings help teams remove the secret and revoke or rotate it., dependency and vulnerability checks via Dependabot and code scanning, supply-chain controls, and organization-wide credential revocation — are aimed at developers and the appsec or platform teams responsible for securing code at scale, while Copilot adds AI-assisted coding with enterprise controls over models, plugins, and MCPMCPModel Context Protocol, a standard for connecting AI applications to external tools and data sources. A compatible server exposes capabilities an assistant can use through a common interface. servers. It sits in the devsecops space, combining source control, CI/CD, and code-scanning in one platform rather than requiring separate tools for each. Launched in 2008, it ships frequently, with its most recent release 11 days ago and 98 releases in the tracked window, indicating active, ongoing development.
GitHub is a web-based platform for version control and collaborative software development using Git repositories.
How GitHub helps
Which of my OAuth apps are still handing out long-lived tokens instead of short-lived ones?
checks whether an app has opted into the short-lived token setting or been switched to always issue them, and flags older SDKs still relying on long-lived flows by their incompatibility with the forced refresh flow
Have I actually cut off a compromised credential everywhere it was used?
runs a bulk revocation by credential type across the enterprise or a single user, and confirms completion through an audit log entry and an email notification to the affected user
Can my organization admins respond to a credential leak without escalating to enterprise owners?
gives organization-level REST API and UI access to the same bulk deauthorization and revocation actions previously restricted to the enterprise level
Which MCP servers and plugins are my developers actually allowed to connect to?
enforces an allowed/denied MCP server list and a restricted marketplace setting centrally, so any unlisted server or plugin source is blocked in the IDE regardless of developer preference
Is my code quality trending in the wrong direction before it becomes a bigger problem?
plots open findings over a chosen date range grouped by health score or severity on the organization dashboard, showing direction of change rather than a single point-in-time count
Languages
Features
Built from GitHub's releases, docs, README and our own runs. “Seen” marks the month we first spotted a release the vendor didn't date. Group names and tags are our labels.
- GitHub covers 1 of the 8 vulnerability assessment methods capabilities we track.
- GitHub covers 1 of the 2 secrets and credential hygiene capabilities we track.
What GitHub offers you
- Command-line interface12
- REST API7
- Web management console4
- Built-in AI assistant3
- Natural-language query3
- Plugin system3
- CI/CD pipeline integration2
- CSV data export2
- Scripting language support2
- Administrative audit log1
- Autonomous investigation and remediation1
- Extension marketplace1
- GraphQL API support1
- Import from a competing product1
- Offline mode1
- Outbound webhooks (the product notifies you)1
- Plugin API support1
- Role-based access control1
- Scheduled jobs1
No capabilities match.
Static application security testing 2 features Vulnerability assessment methods since 2026
AI-Powered Security Detection Rollout shipped Enables programmatic, at-scale rollout of AI-powered security detections for pull requests across an organization.
Shared capability: Static application security testing
release 14 total
- Adds SQL-injection sink models for the Comdb2 C API and flow summaries for Bloomberg BDE codecs and byte-stream deserializers in C/C++ analysis. CodeQL 2.27.2 improves C++, Go, Rust, and JavaScript analysis (2026-10-09) · Oct 2026 · source · release history
-
Improves the
cs/web/missing-x-frame-optionsquery to recognize ASP.NET Core response headers and Content Security Policyframe-ancestorsdirectives as clickjacking protections. CodeQL 2.27.2 improves C++, Go, Rust, and JavaScript analysis (2026-10-09) · Oct 2026 · source · release history -
Adds modeling of the
github.com/coder/websocketimport path in Go analysis (alongside the existingnhooyr.io/websocketpath). CodeQL 2.27.2 improves C++, Go, Rust, and JavaScript analysis (2026-10-09) · Oct 2026 · source · release history -
Adds flow summaries for
native-tls,async-native-tls, andtokio-native-tlsin Rust analysis. CodeQL 2.27.2 improves C++, Go, Rust, and JavaScript analysis (2026-10-09) · Oct 2026 · source · release history -
Adds C++ parsing of regular expressions that use the ECMAScript grammar in
std::regex. CodeQL 2.27.2 improves C++, Go, Rust, and JavaScript analysis (2026-10-09) · Oct 2026 · source · release history -
Adds recognition of the Workflow SDK's
'use workflow'and'use step'directives in JavaScript/TypeScript analysis. CodeQL 2.27.2 improves C++, Go, Rust, and JavaScript analysis (2026-10-09) · Oct 2026 · source · release history
example
-
Report unpinned tags from first-party GitHub-owned Actions (owner github) by removing them from the default trusted set.
!githubCodeQL 2.27.2 improves C++, Go, Rust, and JavaScript analysis (2026-10-09) · Oct 2026 · source -
Filter the security overview coverage view to find all repositories that have NOT yet enabled AI Scan for pull requests, so you can target rollout gaps across your org.
In the GitHub security overview coverage view, enter `code-scanning-ai-scan-pr-scan:not-enabled` in the filter bar to list all repositories where AI Scan for pull requests is not enabled.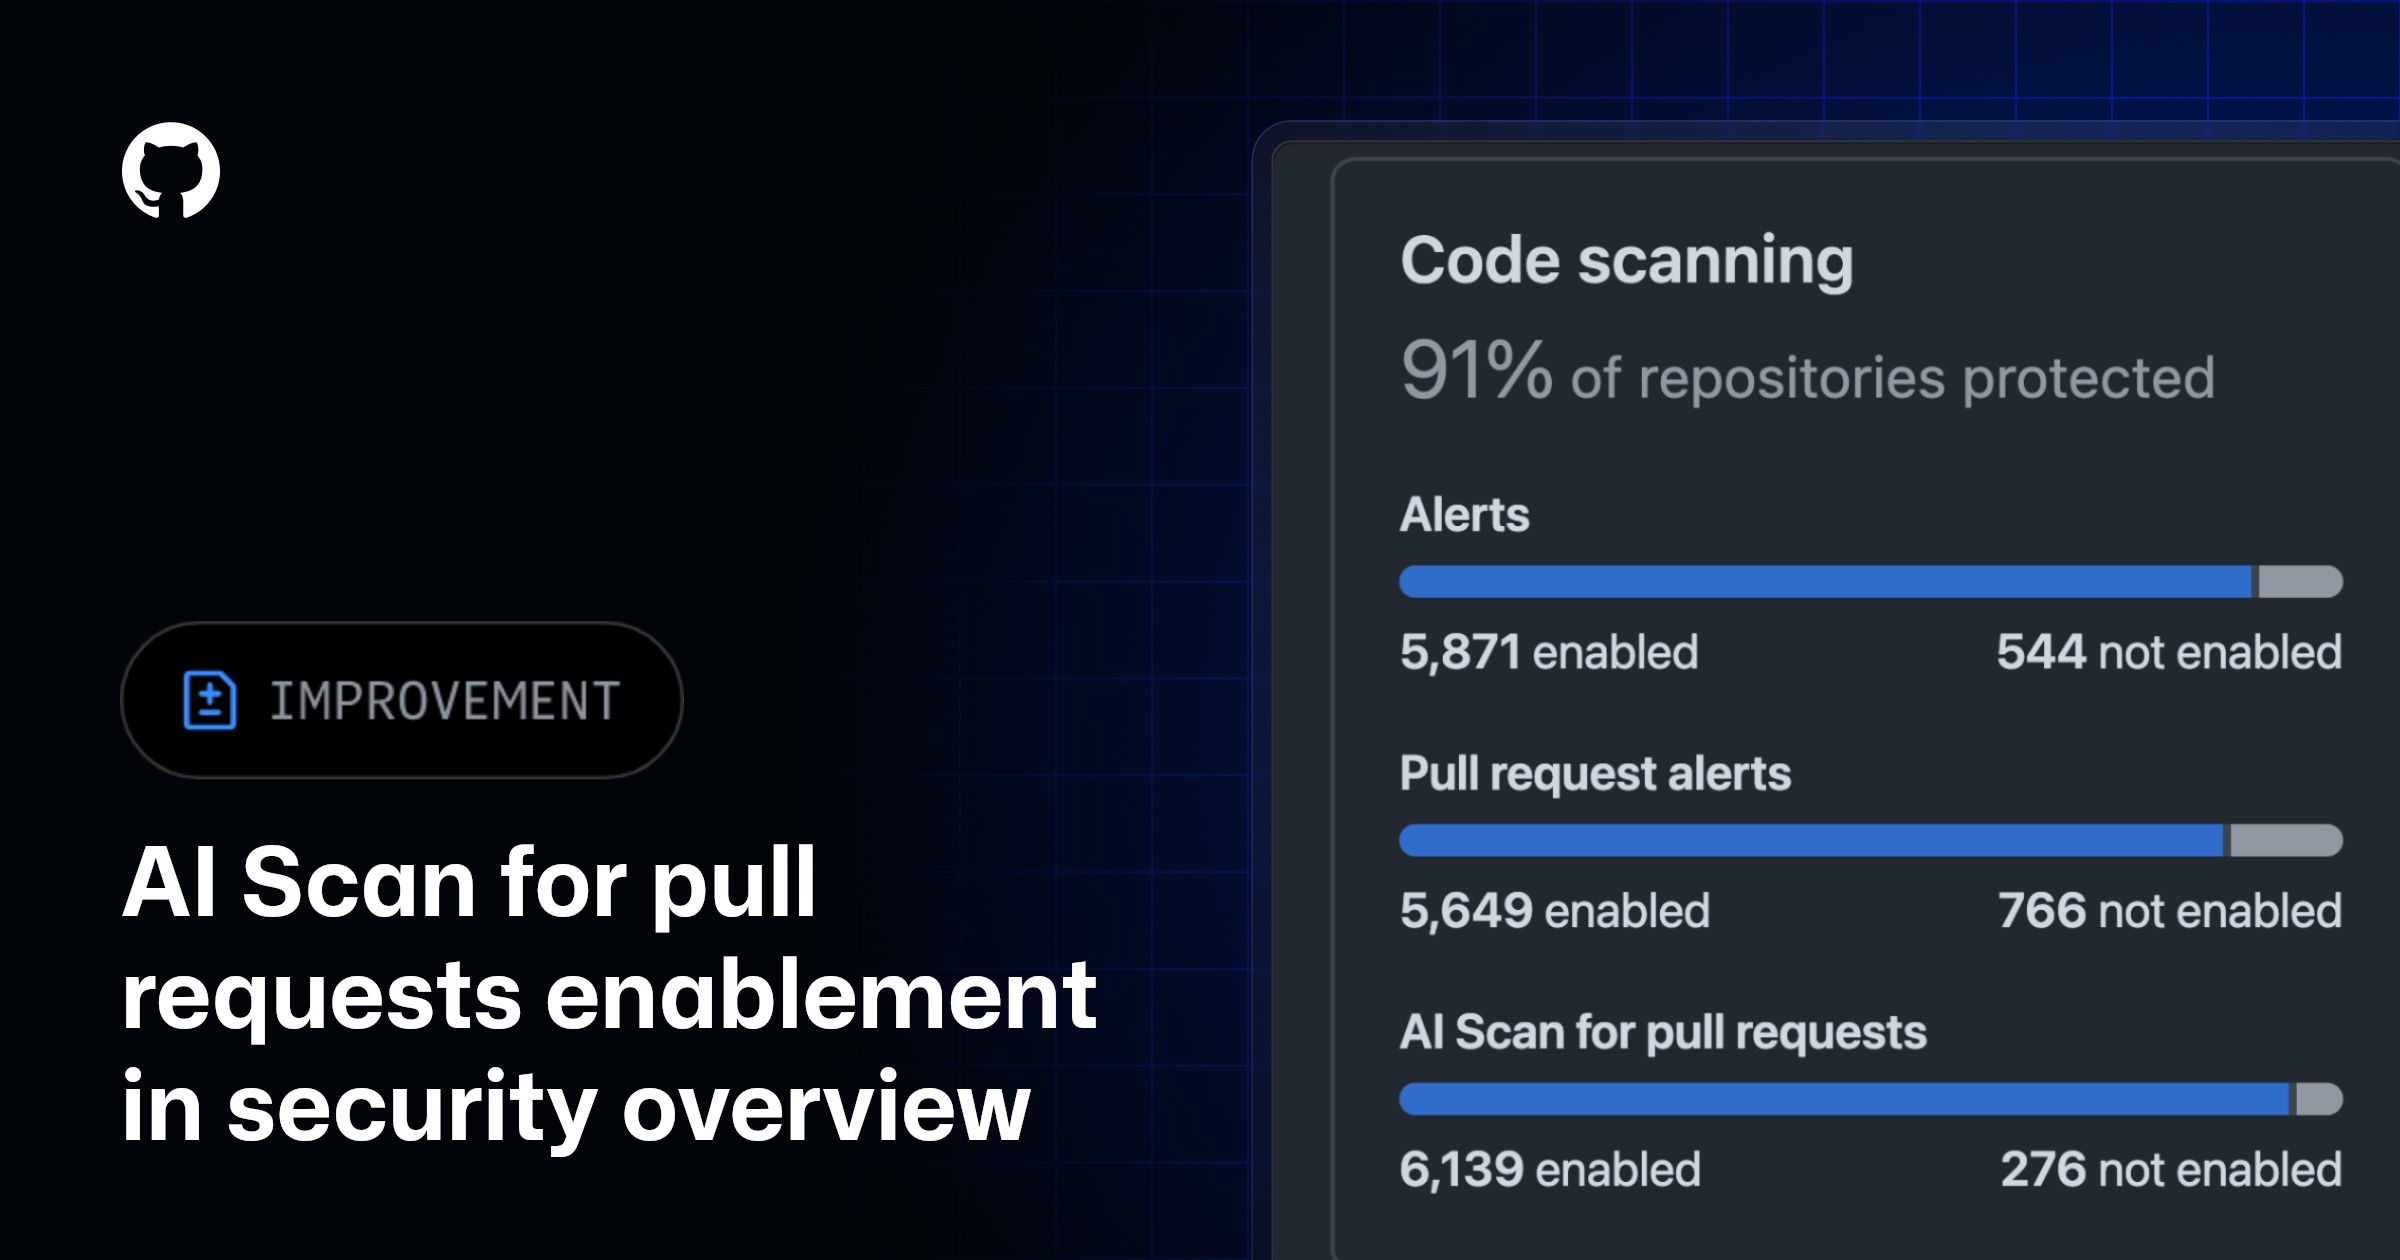 Code scanning AI Scan enablement status in security overview (2026-10-06) · Oct 2026
· source
CodeQL Language and Query Improvements shipped Extends CodeQL's static analysis with updated language support (C/C++ C23 bit-precise integers, Python 3.15, C# positional patterns), new flow sources for Ruby Grape APIs and BlazingMQ C++ classes, proxy/certificate passthrough for C# NuGet in private registries, an opt-in LLM threat model for AI-generated data sources, JSON syntax support for data extension files, and updated Python queries that respect configured threat models.
Shared capability: Static application security testing
Also counts toward: Scripting language support
release 9 total
- C/C++ now supports C23 bit-precise integers (_BitInt(N)). CodeQL 2.27.3 adds Python 3.15 features and JSON data extensions (2026-11-03) · Nov 2026 · source · release history
-
Ruby analysis now treats Grape::API request sub-accessors — including
body.read,body.string,params,GET,POST,cookies,env,query_string, andpath_info— as remote flow sources. CodeQL 2.27.3 adds Python 3.15 features and JSON data extensions (2026-11-03) · Nov 2026 · source · release history -
Adds flow summaries for the BlazingMQ
BloombergLP::bmqa::MessageandMessagePropertiesclasses and their iterators in C/C++. CodeQL 2.27.3 adds Python 3.15 features and JSON data extensions (2026-11-03) · Nov 2026 · source · release history - When private registries are configured, CodeQL now passes proxy and certificate environment variables to the NuGet CLI for C# projects. CodeQL 2.27.3 adds Python 3.15 features and JSON data extensions (2026-11-03) · Nov 2026 · source · release history
-
C# data flow now tracks values through positional patterns in
isexpressions and switch cases. CodeQL 2.27.3 adds Python 3.15 features and JSON data extensions (2026-11-03) · Nov 2026 · source · release history -
Enable an opt-in
aithreat model for LLM-generated data sources, letting you define your own sources via data extensions without any built-in source models. CodeQL 2.27.3 adds Python 3.15 features and JSON data extensions (2026-11-03) · Nov 2026 · source · release history
Single sign-on 1 feature Identity and access since 2026
Enterprise Credential Delegation shipped Allows enterprise-installed GitHub Apps to delegate credentials and automate SSO authorization across multiple organizations.
Shared capability: Single sign-on
Also counts toward: REST API
release 9 total
- Enterprise-level GitHub App installations arrive in GHES 3.24. Enterprise installations for GitHub Apps generally available (2026-10-23) · Oct 2026 · source · release history
-
Adds a set of new Enterprise/Organization GitHub App permissions: Enterprise organization and repository policies permission (read/write) exposing
EnterpriseOwnerInfopolicy fields and REST APIs to update private repository forking, default repository permissions, repository visibility changes, repository… Enterprise installations for GitHub Apps generally available (2026-10-23) · Oct 2026 · source · release history -
Expands Enterprise people permission (read/write) to read
EnterpriseRepositoryInfoincluding repository details throughEnterpriseOwnerInfo.outsideCollaboratorsand add the app to an organization with the owner or member role, and expands Enterprise billing permission (write) to update the member purchasing… Enterprise installations for GitHub Apps generally available (2026-10-23) · Oct 2026 · source · release history - Authorizes a dist-tag operation when the incoming OIDC token matches any one configuration that has Allow npm dist-tag enabled, leaving existing token-based dist-tag management unchanged. Opt-in dist-tag permissions for npm trusted publishing (2026-09-30) · Sep 2026 · source · release history
- Allows staging-only trusted publishing configurations to independently receive dist-tag management permission, without requiring direct publish access. Opt-in dist-tag permissions for npm trusted publishing (2026-09-30) · Sep 2026 · source · release history
-
Adds an opt-in Allow npm dist-tag permission to each trusted publishing configuration, enabling dist-tag operations (promoting to
latest, updatingnextandbetapointers) via short-lived OIDC credentials instead of a long-lived access token.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Opt-in dist-tag permissions for npm trusted publishing (2026-09-30) · Sep 2026 · source · release history
example
-
Grant a GitHub App the permissions needed to manage enterprise rulesets and IP allowlists, replacing classic PAT-based automation.
Settings > Developer settings > GitHub Apps > <your app> > Permissions & events Enterprise repository rulesets: Write Enterprise IP allowlist: Read and write Enterprise organization and repository…Enterprise installations for GitHub Apps generally available (2026-10-23) · Oct 2026 · source -
Enable OIDC-based dist-tag management on a package so CI can promote a release to
latestwithout storing a long-lived npm token.In your package's trusted publishing settings, locate the configuration that handles releases, then enable 'Allow npm dist-tag' on that configuration.Opt-in dist-tag permissions for npm trusted publishing (2026-09-30) · Sep 2026 · source
Secret scanning 1 feature Secrets and credential hygiene since 2026
Secret Scanning Public Monitoring shipped Enables enterprise admins and security managers to receive real-time webhook notifications, query attributed public leak findings via API, and manage alert state (dismiss, reopen, comment) with a full activity timeline for secrets exposed in public locations.
Shared capability: Secret scanning
Also counts toward: REST API, Outbound webhooks (the product notifies you)
release
- Adds alert management for public monitoring: dismiss alerts as Dismissed or Fixed with an optional comment, reopen closed alerts, and review a full activity timeline of state changes. Public monitoring adds triage, validity, API, and webhooks (2026-10-23) · Oct 2026 · source · release history
-
Adds
GET /enterprises/{enterprise}/secret-scanning/public-monitoring-alertsREST API endpoint for enterprise admins and security managers to query attributed public monitoring findings programmatically, returning alert metadata, secret type, attribution, and exposed locations.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Public monitoring adds triage, validity, API, and webhooks (2026-10-23) · Oct 2026 · source · release history -
Adds
secret_scanning_public_monitoring_alertenterprise webhook event to receive real-time notifications whenever a newly detected leak is attributed to your organization. Public monitoring adds triage, validity, API, and webhooks (2026-10-23) · Oct 2026 · source · release history
example
-
Pull all open public monitoring alerts attributed to your enterprise into an incident response script or SIEM.
curl -H "Authorization: Bearer <token>" -H "Accept: application/vnd.github+json" "https://api.github.com/enterprises/<enterprise>/secret-scanning/public-monitoring-alerts?state=open"Public monitoring adds triage, validity, API, and webhooks (2026-10-23) · Oct 2026 · source -
Subscribe your enterprise to real-time leak notifications so your pipeline is triggered the moment a new secret is attributed to your org.
In the enterprise security dashboard, go to Settings > Webhooks > Add webhook, set the payload URL to your endpoint, and select the `secret_scanning_public_monitoring_alert` event.Public monitoring adds triage, validity, API, and webhooks (2026-10-23) · Oct 2026 · source
Other / not yet classified 78 features Features we have not matched to a capability yet. A suggested match is marked.
Enterprise Model Management shipped Enables organization administrators to select, configure, and monitor specific enterprise-grade models for use across the toolchain.
release 30 total
-
Identify enterprise custom model requests across all clients — including IDEs — with the new boolean
is_custom_enterprise_modelfield on eachtotals_by_client[].totals_by_model[]entry. BYOK and enterprise custom models in the Copilot usage API (2026-11-04) · Nov 2026 · source · release history - Pick model providers per workflow from a refreshed model inventory. GitHub Agentic Workflows generally available (2026-10-28) · Oct 2026 · source · release history
- Organization and enterprise owners can turn off image generation by disabling the image generation model using Copilot model policies. Generate and edit images directly in Copilot (2026-10-28) · Oct 2026 · source · release history
-
Enterprise administrators can set Copilot Fusion, at any effort level, as the default model for all Copilot users via Enterprise managed settings.
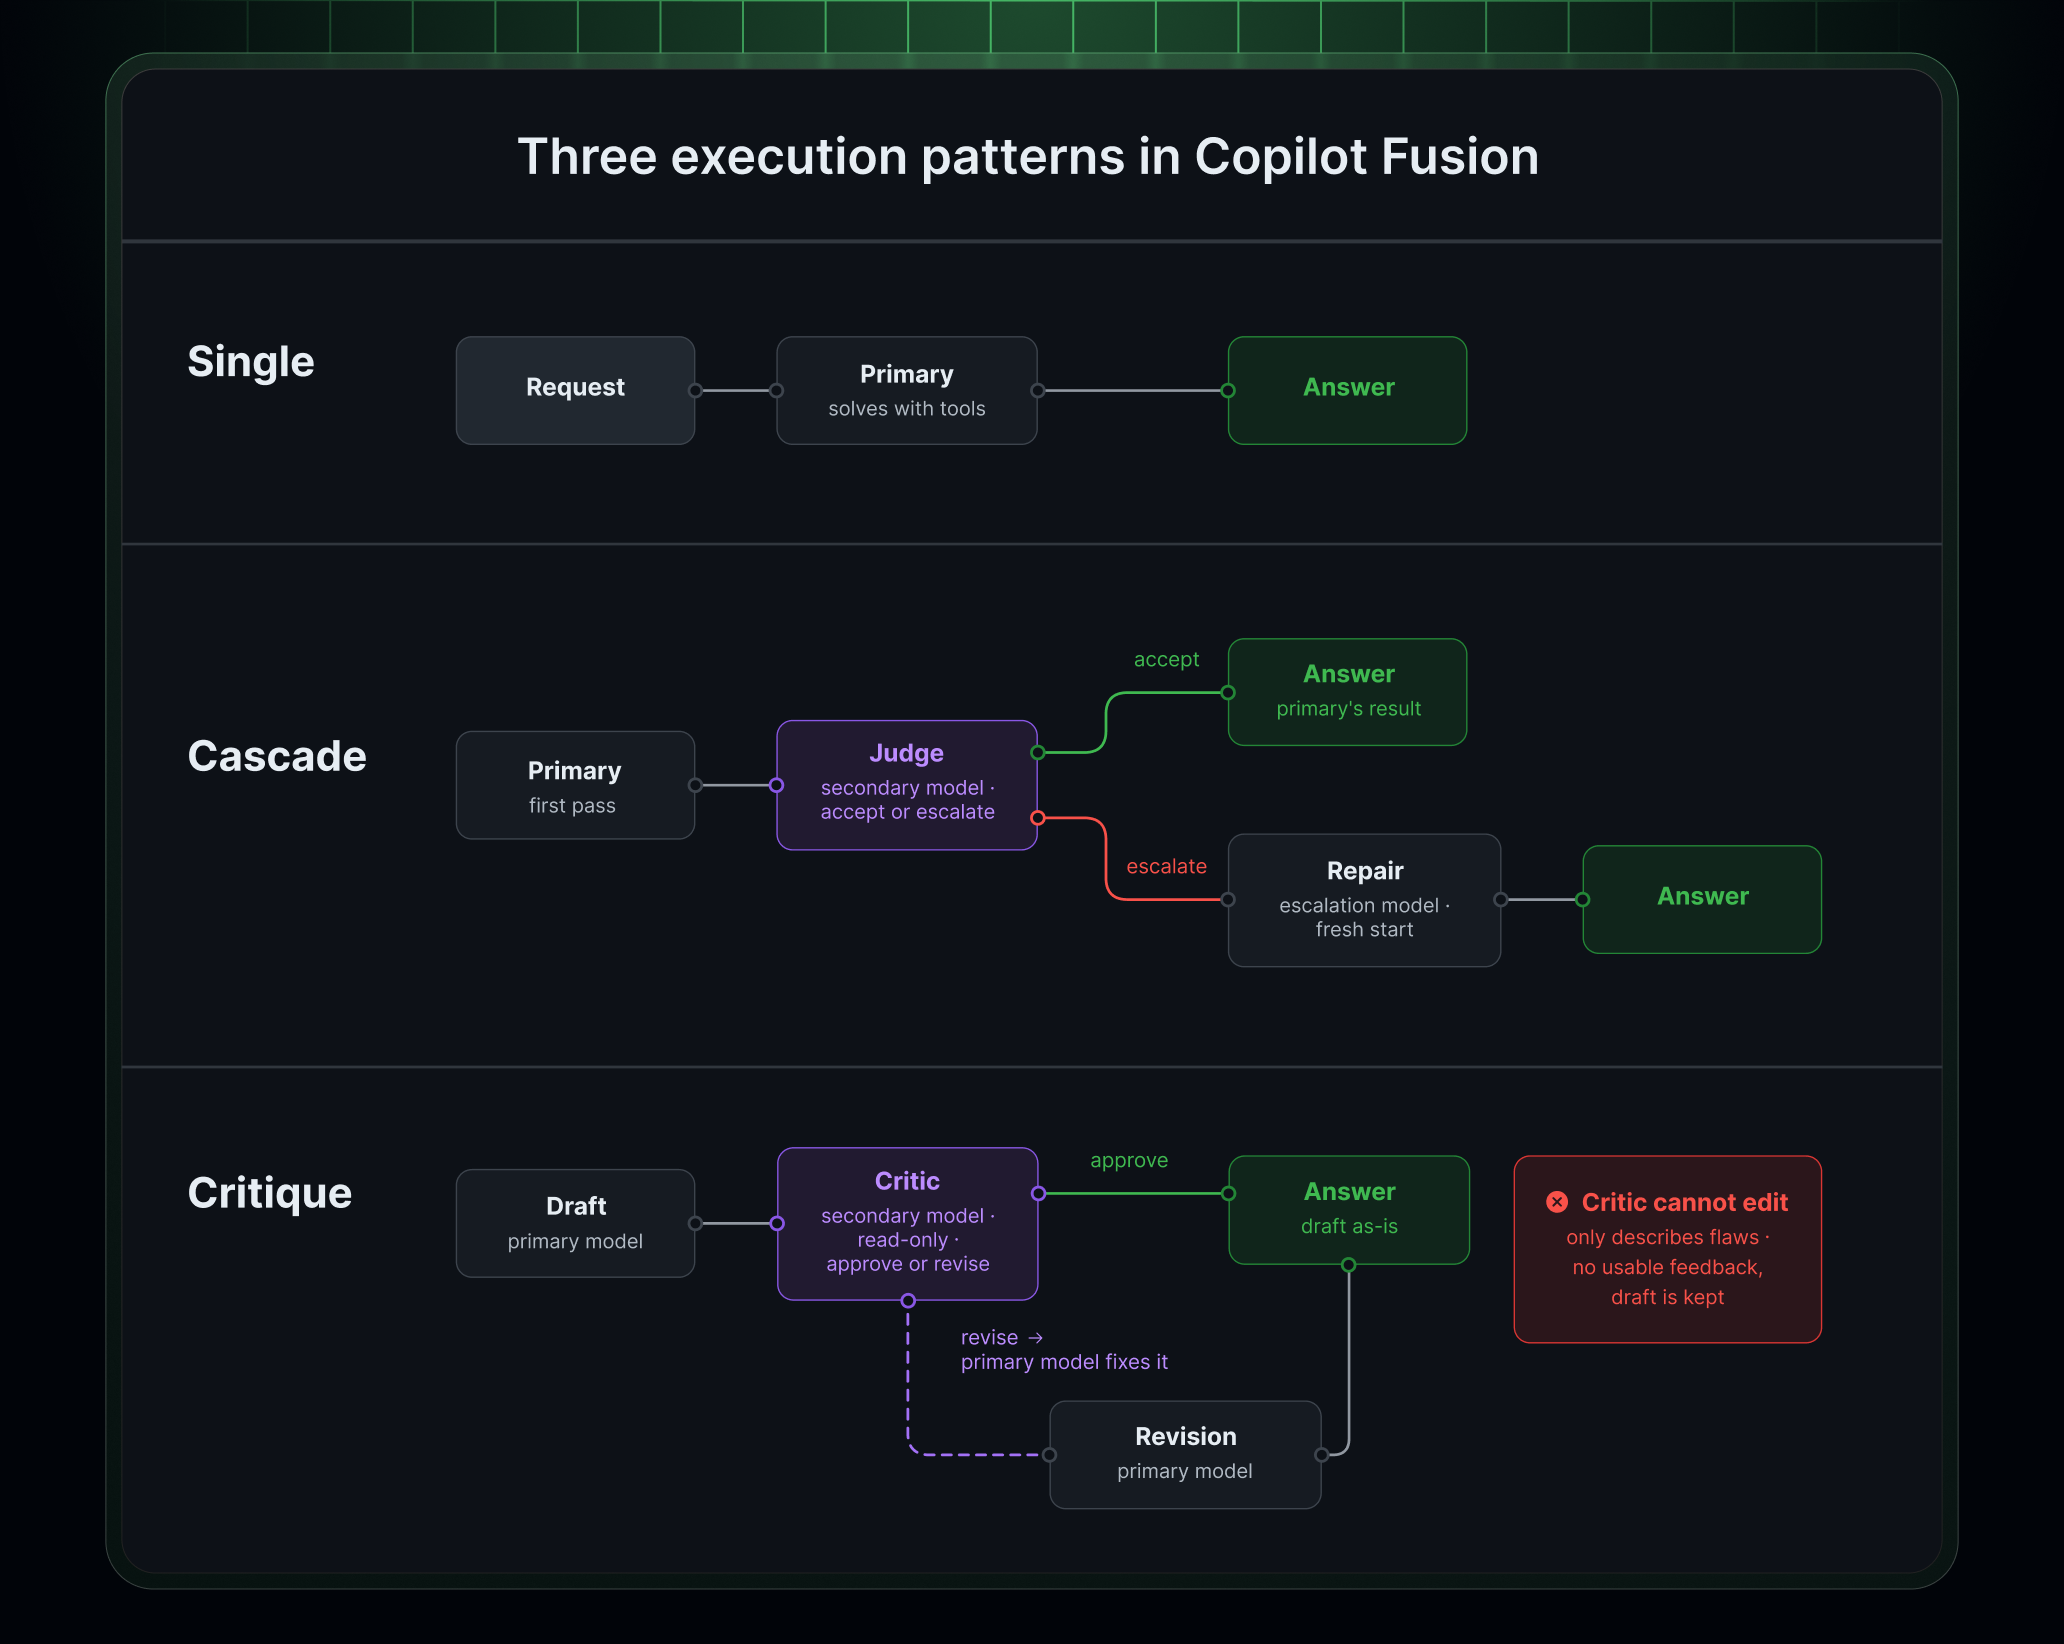 Route and orchestrate models with GitHub Copilot Fusion (2026-10-28) · Oct 2026
· source
· release history
- Enterprise administrators can independently set each model's effective policy state for Copilot Fusion, disabling a model for Fusion without disabling it for all users, via enterprise and organization model policies. Route and orchestrate models with GitHub Copilot Fusion (2026-10-28) · Oct 2026 · source · release history
- Adds GPT-6.1 Terra model selection in the Copilot model picker across Visual Studio Code, Visual Studio, Copilot CLI, GitHub Copilot cloud agent, GitHub Copilot app, github.com, GitHub Mobile (iOS and Android), JetBrains IDEs, Xcode, and Eclipse.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GPT-6.1 Terra in GitHub Copilot (2026-10-26) · Oct 2026 · source · release history
docs
- Made for organizations and enterprises, this plan offers centralized management and Copilot policy control for organization members. Claude Haiku 5.5 Claude Haiku 5.5 seen Oct 2026 · source
example 12 total
-
Separate enterprise custom model token usage from Copilot-hosted model usage across all clients to understand true provider spend.
curl -H 'Authorization: Bearer <token>' \ 'https://api.github.com/enterprises/<enterprise>/copilot/usage?days=28' \ | jq '[.[] | .totals_by_client[] | .totals_by_model[] |…BYOK and enterprise custom models in the Copilot usage API (2026-11-04) · Nov 2026 · source -
Restrict GPT-6.1 Terra from being used org-wide until your team has evaluated it — useful for Enterprise admins who want controlled rollout.
In GitHub Copilot settings, go to Policies > Model policy, find GPT-6.1 Terra, and set it to 'Disabled' to prevent automatic enablement for your organization.GPT-6.1 Terra in GitHub Copilot (2026-10-26) · Oct 2026 · source -
Delegate Copilot model control to individual organizations so each org can manage its own allowed models.
curl -L \ -X PATCH \ -H "Authorization: Bearer <token>" \ -H "Accept: application/vnd.github+json" \ -H "Content-Type: application/json" \…Copilot model policy API for enterprise, orgs, and teams (2026-10-19) · Oct 2026 · source -
Audit which Copilot models are currently permitted across your entire enterprise before rolling out a policy change.
curl -L \ -H "Authorization: Bearer <token>" \ -H "Accept: application/vnd.github+json" \ https://api.github.com/enterprises/{enterprise}/copilot/model-policiesCopilot model policy API for enterprise, orgs, and teams (2026-10-19) · Oct 2026 · source -
Select Gemini 4 Argon for an agentic coding task in Copilot CLI where its edge-case verification gives higher confidence in generated scripts.
In Copilot CLI, open the model picker and select 'Gemini 4 Argon', then run your prompt as normal.Gemini 4 Argon in GitHub Copilot (2026-10-13) · Oct 2026 · source -
As a Copilot Business or Enterprise admin, restrict access to Gemini 4 Argon for your organisation while keeping other models available.
In GitHub org settings, go to Copilot > Policies > Model policy, find 'Gemini 4 Argon', and set it to 'Disabled'.Gemini 4 Argon in GitHub Copilot (2026-10-13) · Oct 2026 · source
Code Review Capabilities shipped Extends the agent's ability to analyze code changes and provide assessment summaries within pull request workflows.
release 21 total
- Dreaming runs three dream types: personal memory curation, repository customization (which proposes skill and instruction updates in pull requests), and code review customization that converts recurring accepted feedback into Copilot code review guidance. GitHub intelligence puts your code, context, and history to work (2026-10-28) · Oct 2026 · source · release history
-
Run
/security-reviewon your current local changes to catch new issues before opening a pull request, with the extension flagging when code has changed since the last review.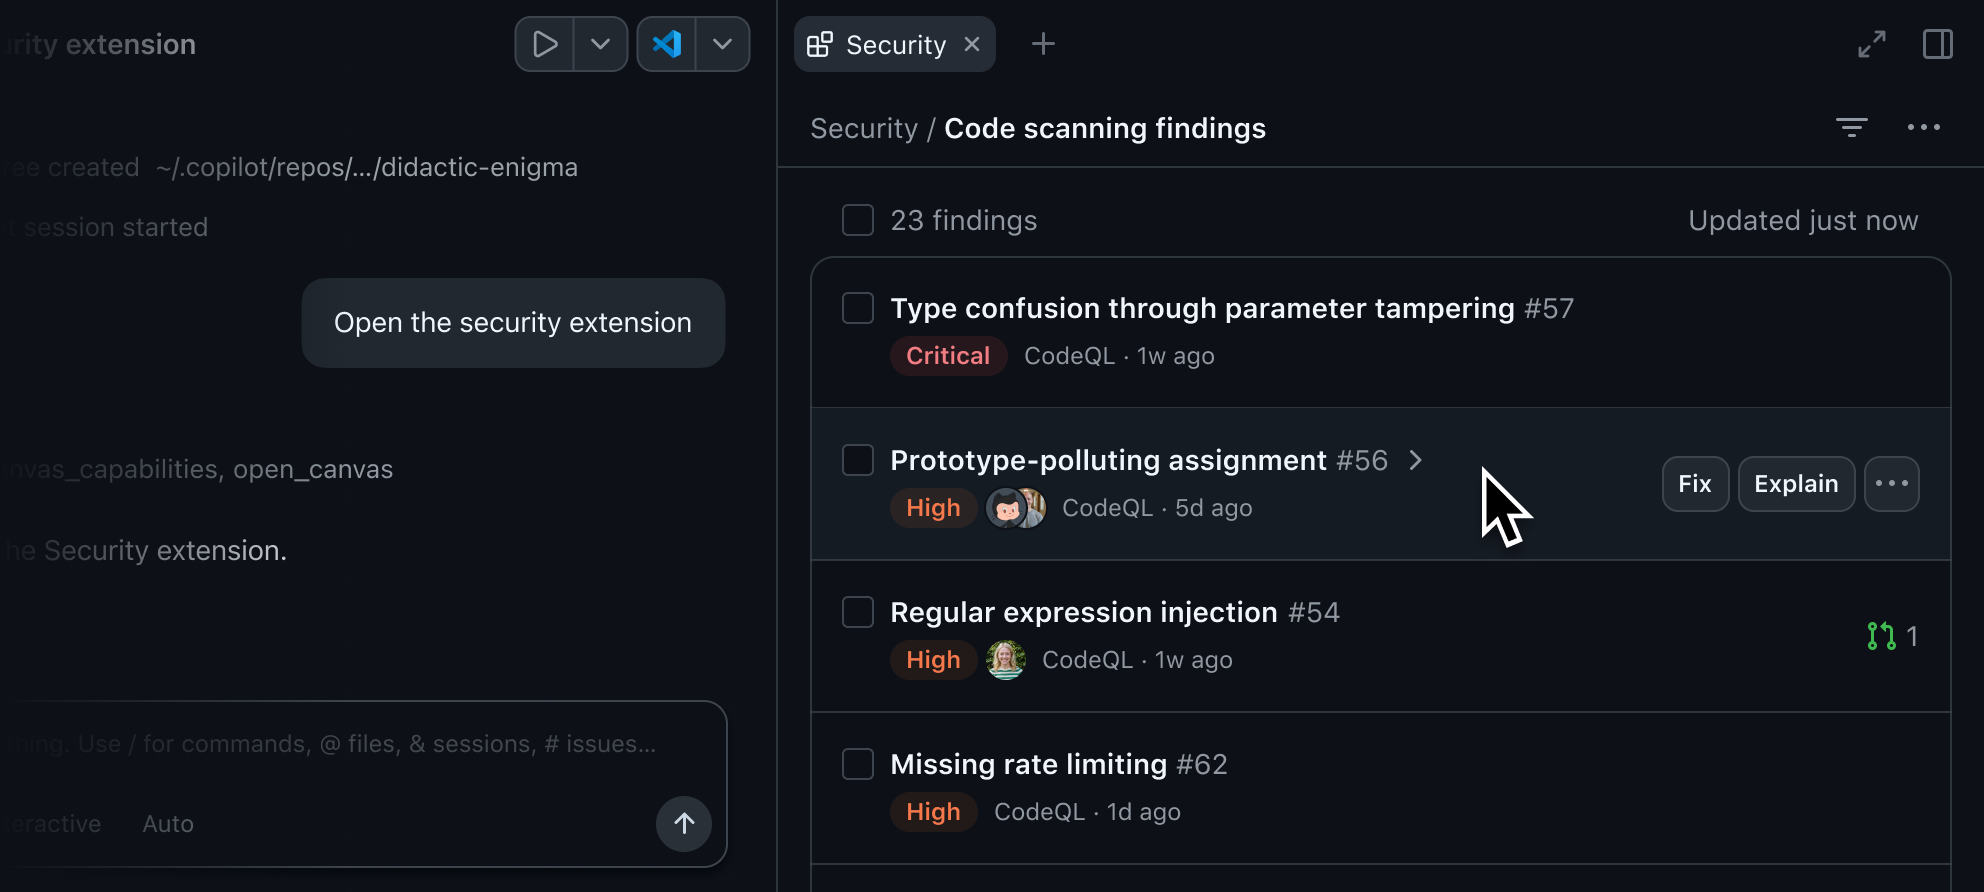 Security extension for the GitHub Copilot app (2026-10-28) · Oct 2026
· source
· release history
- Adds Git agent support for exploring pull requests in Copilot Chat by attaching a PR as context from the Git Repository window, returning a summary with navigable links to comments and files — requires connecting GitHub or Azure DevOps MCP servers.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub Copilot in Visual Studio — September update (2026-10-23) · Oct 2026 · source · release history
- AI Scan findings appear alongside CodeQL results on the Conversation and Files changed tabs with an AI indicator, and can include an explanation of the security risk and a suggested autofix. AI Scan for pull requests generally available (2026-10-15) · Oct 2026 · source · release history
- Adds AI Scan for pull requests as a generally available capability that finds vulnerabilities in PR changes for languages and frameworks CodeQL does not currently cover, including PHP, Shell/Bash, Terraform configuration (HCL), Dockerfiles, JSP for Java, and Blazor for C#.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ AI Scan for pull requests generally available (2026-10-15) · Oct 2026 · source · release history
- Upgrades the Critique workflow to use tool-based workspace inspection instead of text summaries, and adds parallel critic models. HydraFusion updates and new Max option (2026-10-14) · Oct 2026 · source · release history
example
-
Scan your uncommitted changes for new issues before opening a pull request, without waiting for CI to run code scanning.
/security-reviewSecurity extension for the GitHub Copilot app (2026-10-28) · Oct 2026 · source -
Enable AI Scan on a repository so it automatically runs on every pull request alongside CodeQL.
In the repository, go to Settings > Code security > Code scanning, then enable the 'AI Scan' setting under the code scanning configuration.AI Scan for pull requests generally available (2026-10-15) · Oct 2026 · source -
Restrict Copilot code review requests to users holding an org- or enterprise-issued license, blocking personal or external licenses org-wide.
In your organization settings, go to Copilot -> Policies and enable 'Only allow Copilot code review to be triggered by authorized users'.Copilot code review: New organization billing options and controls (2026-10-08) · Oct 2026 · source -
Run an AI-powered security review of active changes — including the new secret-classifier checks — before committing or opening a pull request.
/security-reviewPurpose-built model for leaked secret detection (2026-10-07) · Oct 2026 · source -
Override the default effort level back to Lite for a specific repository whose reviewers prefer lighter feedback.
In your repository settings, go to Copilot -> Code review and set the review effort level to `Lite`.Copilot code review: API support and new default effort level (2026-10-02) · Oct 2026 · source -
Use Codex plan mode to review and shape an agent's approach before it touches any files — useful for high-impact refactors or unfamiliar codebases.
In the Copilot tool window, open a Codex agent session, describe your task, and select 'Plan' mode. Review the generated plan, refine the steps, then approve it to let the agent begin implementation.New features and improvements in Copilot for JetBrains (2026-09-23) · Sep 2026 · source
Copilot Adoption and Engagement Reporting shipped Provides detailed metrics on user engagement, feature usage, and adoption phases for Copilot across the organization.
release 21 total
-
Track per-user local BYOK activity with the new
used_local_byokfield in user-level Copilot usage reports.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ BYOK and enterprise custom models in the Copilot usage API (2026-11-04) · Nov 2026 · source · release history - GitHub's Copilot usage metrics API now surfaces all four new BYOK and custom-model fields in both enterprise and organization reports, at user and aggregate level, in 1-day and 28-day reports. BYOK and enterprise custom models in the Copilot usage API (2026-11-04) · Nov 2026 · source · release history
-
Each
totals_by_cliententry also includestotals_by_model, which breaks down request and token metrics by model and adds amodel_selection_modefield with valuesuser_selected,auto,product_selected,other, orunknown. Usage metrics API adds usage from tools like OpenCode (2026-10-23) · Oct 2026 · source · release history -
Each
totals_by_cliententry includesclient(tool identifier such asopencode,claude_code,codex,zed,copilot_cli,github_app,cloud_agent,code_review,vscode, orjetbrains; unrecognized clients grouped asother),request_count,session_count, andtoken_usage(prompt tokens, output… Usage metrics API adds usage from tools like OpenCode (2026-10-23) · Oct 2026 · source · release history -
In 28-day aggregated reports,
totals_by_clientappears inside eachday_totalsentry, enabling day-level per-client breakdowns. Usage metrics API adds usage from tools like OpenCode (2026-10-23) · Oct 2026 · source · release history -
Adds
totals_by_clientarray to the Copilot usage metrics API for enterprise, organization, enterprise-user, and organization-user 1-day and 28-day reports, exposing per-tool model traffic.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Usage metrics API adds usage from tools like OpenCode (2026-10-23) · Oct 2026 · source · release history
docs
- Prepare your organization to evaluate Advanced Security against clear security and purchasing goals. seen Oct 2026 · source
example
-
Compare model request and token volume across all Copilot-connected tools in your org to inform tool support and governance decisions.
curl -H 'Authorization: Bearer <token>' -H 'Accept: application/vnd.github+json' 'https://api.github.com/orgs/<org>/copilot/metrics?report=1-day' | jq '.totals_by_client[] | {client: .client,…Usage metrics API adds usage from tools like OpenCode (2026-10-23) · Oct 2026 · source -
Break down per-tool usage by model and selection mode across the 28-day enterprise report to see whether developers are using auto-selected or user-chosen models in each tool.
curl -H 'Authorization: Bearer <token>' -H 'Accept: application/vnd.github+json' 'https://api.github.com/enterprises/<enterprise>/copilot/metrics?report=28-day' | jq '.day_totals[] | {date: .date,…Usage metrics API adds usage from tools like OpenCode (2026-10-23) · Oct 2026 · source
Agent Plugin Support shipped Enables the creation and management of plugins that can run across multiple Copilot surfaces including VS Code, CLI, and JetBrains.
Also counts toward: Plugin API support, Plugin system
release 17 total
-
Discover, create, and manage agent customizations — skills, MCP servers, plugins — from the Customizations Marketplace in the Agents window sidebar or via the
Chat: Open Customizationscommand (enabled by default in preview), and register plugin marketplaces and enable default plugins at the repository level via…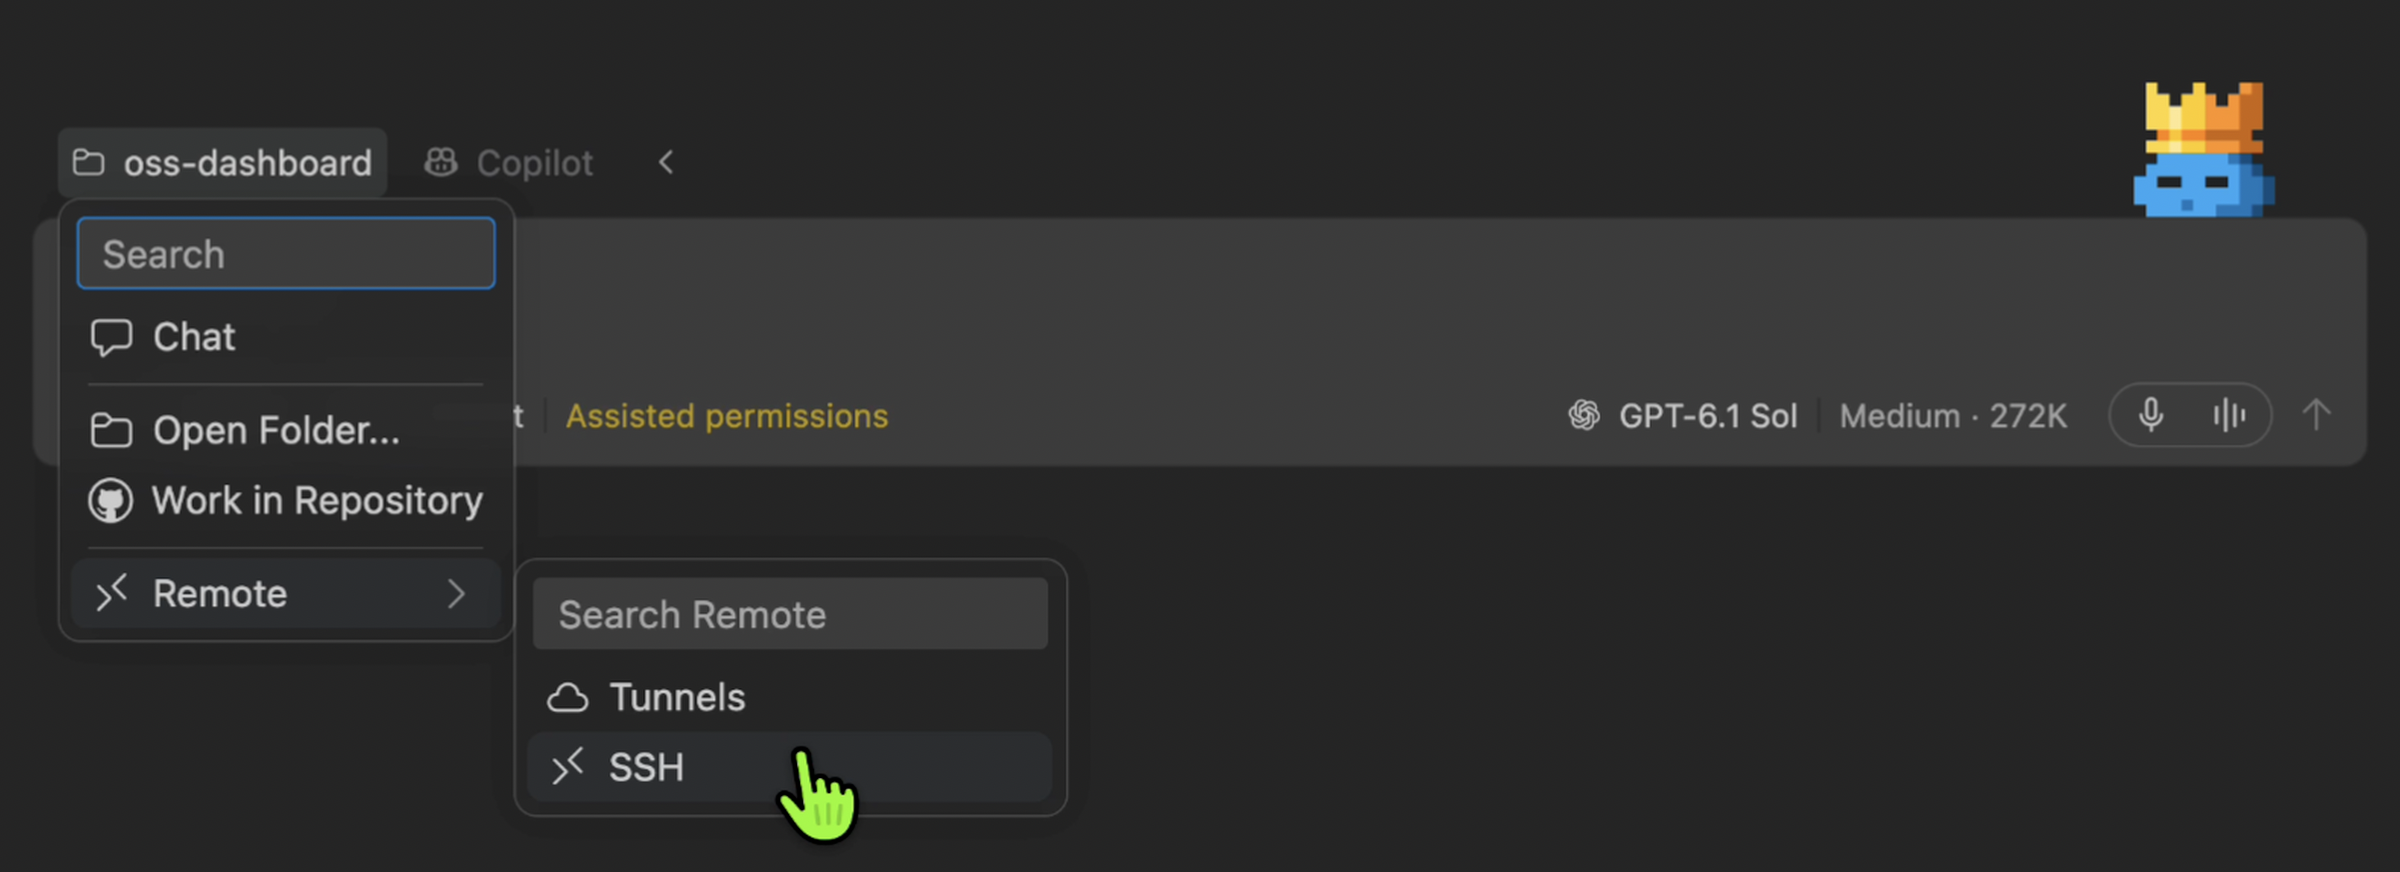 GitHub Copilot in VS Code, Universe releases (2026-10-28) · Oct 2026
· source
· release history
-
Install the security extension with
copilot plugin install github-security@awesome-copilotin the terminal, or search forgithub-securityin the Copilot app's Customize panel and click Install.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Security extension for the GitHub Copilot app (2026-10-28) · Oct 2026
· source
· release history
- The security extension is available in public preview on github.com and GitHub Enterprise Cloud with data residency; GitHub Enterprise Server is not supported. Security extension for the GitHub Copilot app (2026-10-28) · Oct 2026 · source · release history
-
Install GitHub Copilot CLI through the VS Code installer on Windows, when adding VS Code to your path on macOS, or by running
copiloton Linux. GitHub Copilot in VS Code, Universe releases (2026-10-28) · Oct 2026 · source · release history - GitHub Copilot has ended support for JetBrains IDE 2025.1; JetBrains IDE 2025.2 or later is now required to use the plugin. New controls and chat improvements in Copilot for JetBrains (2026-10-10) · Oct 2026 · source · release history
- Adds a new MCP setting to disable automatic server startup for Copilot and Claude, giving administrators control over when configured tools become active.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New controls and chat improvements in Copilot for JetBrains (2026-10-10) · Oct 2026 · source · release history
docs
- Adding MCP servers for GitHub Copilot CLI Extend Copilot's capabilities by connecting Model Context Protocol (MCP) servers to provide additional tools and context. Administer Copilot CLI Administering Copilot CLI for your enterprise Control the use of Copilot CLI within your enterprise. docs update · Oct 2026 · source
- About enterprise-managed plugin standards Enterprise administrators can centrally define plugin policies for users, ensuring consistent plugin availability. seen Oct 2026 · source
- Adding custom instructions for GitHub Copilot CLI Give Copilot additional context on how to understand your project and how to build, test and validate its changes. docs update · Oct 2026 · source
example
-
Install the GitHub security extension from the terminal so you can immediately browse code scanning alerts in the Copilot app.
copilot plugin install github-security@awesome-copilotSecurity extension for the GitHub Copilot app (2026-10-28) · Oct 2026 · source -
Disable automatic MCP server startup so Copilot and Claude tools only become active when you explicitly enable them — useful in restricted or air-gapped environments.
In the JetBrains IDE, go to Settings > GitHub Copilot > MCP and disable 'Automatic server startup' for Copilot and Claude.New controls and chat improvements in Copilot for JetBrains (2026-10-10) · Oct 2026 · source -
Enable dynamic workflows in Copilot CLI to orchestrate a multi-agent incident investigation across logs and telemetry.
gh copilot --experimentalDynamic workflows in Copilot CLI and the Copilot app (2026-10-01) · Oct 2026 · source -
Reach the new Customize tab to discover and install MCP servers, plugins, skills, and canvases for your team.
1. Open the GitHub Copilot app. 2. Select 'Customize' in the top navigation. 3.GitHub Copilot app Customize tab is generally available (2026-08-25) · Aug 2026 · source
Usage Budgeting and Billing shipped Offers controls for monitoring, budgeting, and billing for cloud agent credits and sandbox usage across the organization.
release 14 total
- GitHub Enterprise now includes Copilot access for every licensed user, replacing separate seat and usage tracking with a single enterprise budget model where AI usage is metered from the first request.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub Enterprise now includes access to GitHub Copilot (2026-10-28) · Oct 2026 · source · release history
-
Get a fuller AI credit spend picture using
gh aw forecast, which now includes threat detection credits and monthly ranges and is no longer experimental. GitHub Agentic Workflows generally available (2026-10-28) · Oct 2026 · source · release history - Shared automations are billed to the organization or user that owns the repository rather than to the creator, and actions are attributed to Copilot rather than an individual user. Build shared workflows for your team with Copilot Automations (2026-10-28) · Oct 2026 · source · release history
- Adds CSV download of GitHub Code Quality license usage from the Licensing section of the Billing and licensing page, available on GitHub Team and GitHub Enterprise Cloud.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Download GitHub Code Quality license usage as a CSV (2026-10-15) · Oct 2026 · source · release history
- AI Scan for pull requests consumes Code Security AI Credits, with usage visible in the AI usage section of enterprise billing under the Advanced Security product; SKU-level budgets for Code Security AI Credits can also be set. AI Scan for pull requests generally available (2026-10-15) · Oct 2026 · source · release history
- CSV report includes each active committer consuming a Code Quality license, the repositories receiving their commits in the last 90 days, and whether each committer is unique to a single repository or organization. Download GitHub Code Quality license usage as a CSV (2026-10-15) · Oct 2026 · source · release history
docs
- Choosing your enterprise's plan for GitHub Copilot Choose between Copilot Business and Copilot Enterprise. seen Sep 2026 · source
example 7 total
-
Check projected AI credit spend, including threat detection costs, before committing to a new agentic workflow rollout.
gh aw forecastGitHub Agentic Workflows generally available (2026-10-28) · Oct 2026 · source -
Let an org admin gate shared automations to prevent unintended AI credit usage against the organization budget.
In your organization settings, go to Copilot > Policies and enable 'Allow use of Copilot cloud agent billed to the organization'.Build shared workflows for your team with Copilot Automations (2026-10-28) · Oct 2026 · source -
Download a Code Quality license usage report to identify committers unique to a single repo where disabling Code Quality could free up licenses.
In your organization or enterprise, go to Billing and licensing > Licensing > Code Quality card > Download CSV.Download GitHub Code Quality license usage as a CSV (2026-10-15) · Oct 2026 · source -
Cap spend on Code Security AI Credits at the enterprise level to avoid unexpected billing.
In the enterprise account, go to Billing & licensing > AI usage > Advanced Security, then set a SKU-level budget for Code Security AI Credits.AI Scan for pull requests generally available (2026-10-15) · Oct 2026 · source -
Find the budget covering a specific user in a large enterprise without scrolling through every entry.
In GitHub billing settings, go to 'Budgets and alerts', type the user's name in the search box, and use the 'Scope' menu to select 'Organizations' to confirm which budget applies.Search and filter for budgets now available (2026-10-13) · Oct 2026 · source -
Cap spending on AI push protection and secret-classifier checks before opting into the public preview.
In the GitHub UI: Billing and licensing > Budgets and alerts > New budget > SKU-level budget > Product: Advanced Security > SKU: Secret Protection AI Credits > Enable 'Stop usage when budget limit is…Purpose-built model for leaked secret detection (2026-10-07) · Oct 2026 · source
Private Vulnerability Reporting Controls shipped Provides structured intake forms, rate limiting, trusted-reporter allowlists, CWE requirements, AI-disclosure checkboxes, and custom daily caps for private vulnerability reports submitted to a repository.
release 16 total
-
Custom pattern API now returns
422instead of500for requests rejected due to invalid arguments, letting integrations distinguish input errors from server failures. Updates to GitHub secret scanning (2026-10-20) · Oct 2026 · source · release history - Adds new endpoint to return the enforced form schema when REST API submissions do not match. Structured forms for private vulnerability reports (2026-10-01) · Oct 2026 · source · release history
-
Repositories with a
SECURITY.mdsecurity policy now show reporters a banner linking to it before they submit a private vulnerability report. Structured forms for private vulnerability reports (2026-10-01) · Oct 2026 · source · release history -
If you add a custom
VULNERABILITY_REPORT.ymlform, reports submitted through the REST API must match it — API submissions that do not match will receive an error. Structured forms for private vulnerability reports (2026-10-01) · Oct 2026 · source · release history - Default structured form now requires four fields from reporters: summary, details, proof of concept (minimum 150 characters), and impact. Structured forms for private vulnerability reports (2026-10-01) · Oct 2026 · source · release history
- Adds a new REST API endpoint that returns the form a repository enforces, surfaced in error responses when an API submission does not match the custom form. Structured forms for private vulnerability reports (2026-10-01) · Oct 2026 · source · release history
example
-
Enforce a structured vulnerability report form with minimum detail requirements across all repositories in your organization.
# .github/VULNERABILITY_REPORT.yml in your org's .github repo name: Vulnerability Report description: Report a security vulnerability body: - type: textarea id: summary attributes: label: Summary…Structured forms for private vulnerability reports (2026-10-01) · Oct 2026 · source -
Require reporters to assign a CWE before submitting, and enforce the setting across your organization via policy.
In the repository, go to Settings > Advanced Security > Private vulnerability reporting and enable the option to require a CWE.Structured forms for private vulnerability reports (2026-10-01) · Oct 2026 · source -
Set a custom daily reporting cap for your repository to throttle bulk submissions while still accepting legitimate reports.
1. Go to your repository on GitHub. 2. Click Settings > Advanced Security. 3. Click Settings next to 'Private vulnerability reporting'. 4. Enter your desired daily overall reporting limit. 5.Rate limits for private vulnerability reports (2026-10-01) · Oct 2026 · source -
Require reporters to specify a Common Weakness Enumeration before submitting reports in an organization.
In the console, go to Settings > Advanced Security > Private vulnerability reporting and enable 'Require CWE'Structured forms for private vulnerability reports (2026-10-01) · Oct 2026 · source -
Allow trusted researchers to bypass the new daily report limits so their valid findings are not blocked.
Go to your repository's settings, select Advanced Security , and click Settings next to “Private vulnerability reporting.”Rate limits for private vulnerability reports (2026-10-01) · Oct 2026 · source -
Add a trusted security researcher to the allow list so their reports are never blocked by rate limits.
1. Go to your repository on GitHub. 2. Click Settings > Advanced Security. 3. Click Settings next to 'Private vulnerability reporting'. 4.Rate limits for private vulnerability reports (2026-10-01) · Oct 2026 · source
BYOK Model Support shipped Allows users to bring their own API keys for specific models like Claude and Ollama, integrating them into the Copilot agent flow.
release 17 total
-
Count distinct users running local BYOK models per day, calendar week, and calendar month with the new
daily_active_local_byok_users,weekly_active_local_byok_users, andmonthly_active_local_byok_usersaggregate fields. BYOK and enterprise custom models in the Copilot usage API (2026-11-04) · Nov 2026 · source · release history -
Break down local BYOK session, request, prompt, and token counts by
byok_kind(local_managed,local_user,local_auto, orremote_user) and surface (copilot_cliorcopilot_app) using the newtotals_by_local_byokfield. BYOK and enterprise custom models in the Copilot usage API (2026-11-04) · Nov 2026 · source · release history - Introduces Bring Your Own Model (BYOM) in preview, enabled by default across Community, Professional, and Enterprise editions, supporting Microsoft Foundry, OpenAI, Anthropic, and Ollama providers — works with or without a GitHub sign-in. GitHub Copilot in Visual Studio — September update (2026-10-23) · Oct 2026 · source · release history
- BYOM now requires the new Agent (Preview) harness built on the GitHub Copilot SDK; the previous Ask and Agent modes no longer support BYOM, and previously configured Ollama models must be re-added after updating. GitHub Copilot in Visual Studio — September update (2026-10-23) · Oct 2026 · source · release history
-
Adds
/modelcommand in GitHub Copilot CLI (v1.0.94-0+) to discover models from a running local Ollama instance alongside configured and cloud models.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Discover local models in GitHub Copilot CLI (2026-10-07) · Oct 2026 · source · release history - Enables adding a discovered local model for the current session — with provider and endpoint review — via Add and use for this session or Add without switching, without restarting the CLI. Discover local models in GitHub Copilot CLI (2026-10-07) · Oct 2026 · source · release history
example
-
Pull a 1-day enterprise usage report and check which users made at least one local BYOK request — useful for auditing BYOK policy compliance.
curl -H 'Authorization: Bearer <token>' \ 'https://api.github.com/enterprises/<enterprise>/copilot/usage?days=1' \ | jq '[.[] | select(.used_local_byok == true) | {login, used_local_byok,…BYOK and enterprise custom models in the Copilot usage API (2026-11-04) · Nov 2026 · source -
Discover and add a local Ollama model to your Copilot CLI session without restarting — useful when you want to test a locally hosted model mid-workflow.
/modelDiscover local models in GitHub Copilot CLI (2026-10-07) · Oct 2026 · source -
Add a supported local model provider in the GitHub Copilot app so it appears in the model picker alongside cloud models.
In the GitHub Copilot app, go to Settings > Model providers and add your local Ollama provider.Discover local models in GitHub Copilot CLI (2026-10-07) · Oct 2026 · source -
Enable Claude Fable 5.1 for your organization as a Copilot Enterprise or Business admin so team members can select it in the model picker.
In GitHub Copilot settings for your organization, navigate to Policies, locate the 'Claude Fable 5.1' policy, and toggle it on.Claude Fable 5.1 is generally available in GitHub Copilot (2026-09-01) · Sep 2026 · source
Asynchronous Agent Sessions shipped Enables Copilot agent workflows to run asynchronously in the cloud with results available for inspection, continuation, or handoff across different surfaces.
release 13 total
-
Connect GitHub Copilot to JetBrains Air via the Agent Client Protocol (ACP) to delegate coding tasks, track parallel agent sessions, and review changes in-context inside your JetBrains IDE.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
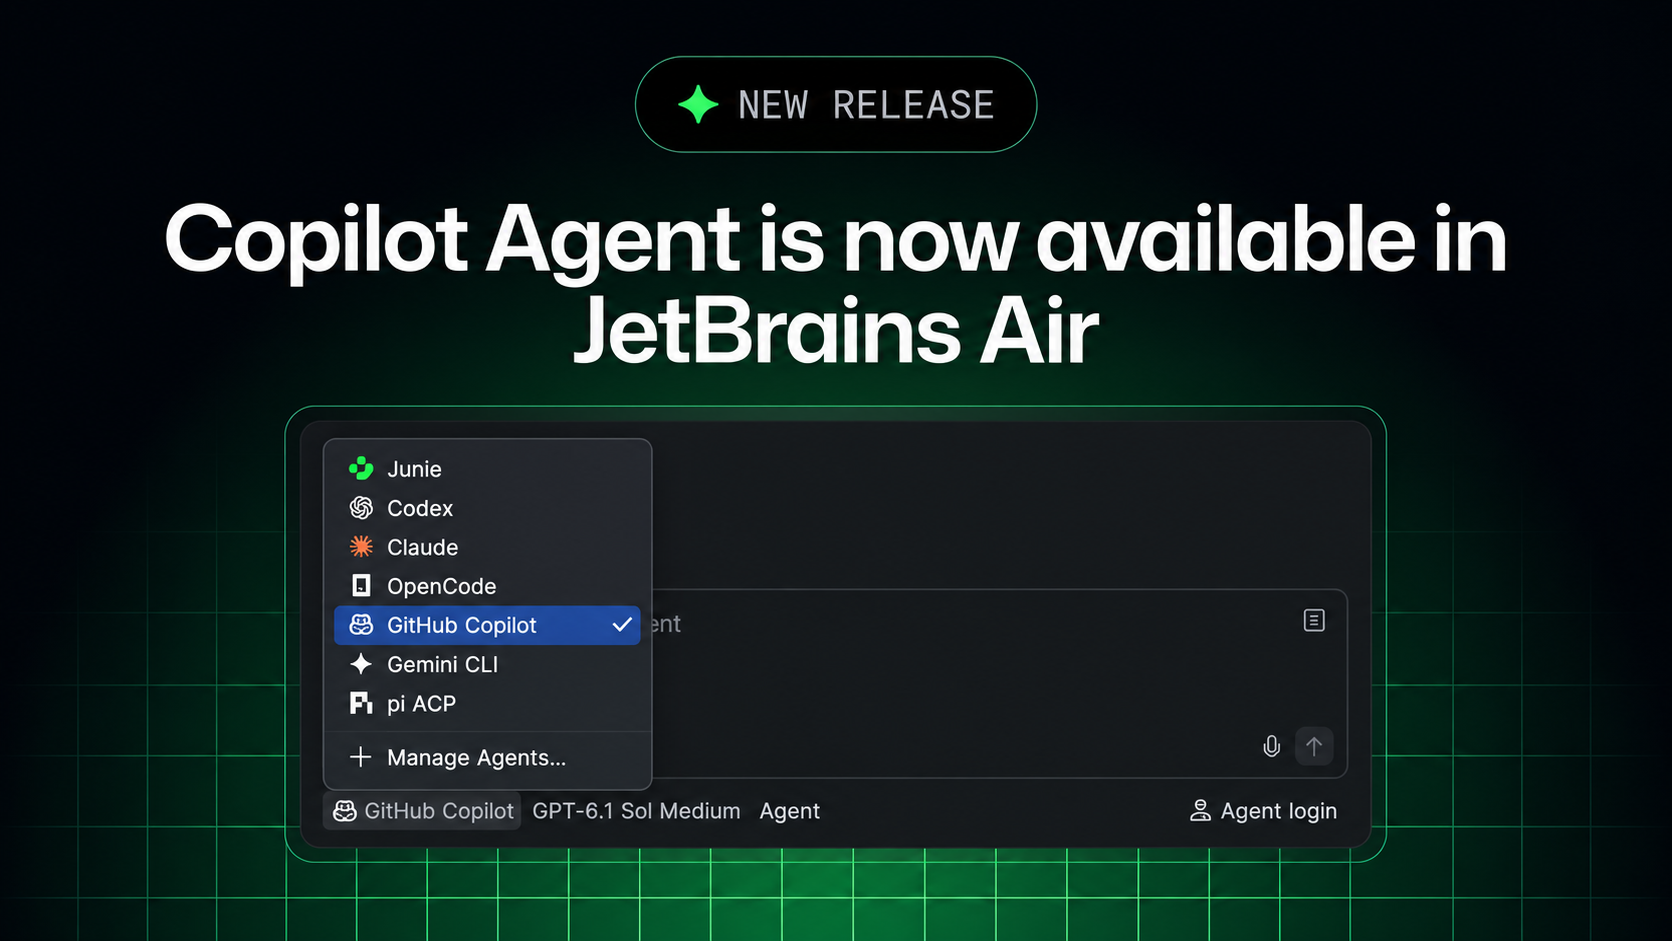 GitHub Copilot is now available in JetBrains Air (2026-11-03) · Nov 2026
· source
· release history
- Link your GitHub account for cloud tasks from the browser by navigating to Settings > VCS Providers in JetBrains Air, then selecting a repository, remote branch, and GitHub Copilot as the agent. GitHub Copilot is now available in JetBrains Air (2026-11-03) · Nov 2026 · source · release history
-
Enables dynamic workflows in the Copilot CLI via the
--experimentalcommand-line option or/experimental onin an interactive session, allowing code-defined multi-agent orchestration.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Dynamic workflows in Copilot CLI and the Copilot app (2026-10-01) · Oct 2026 · source · release history - Supports pause-and-resume checkpoints in dynamic workflows, letting practitioners review intermediate findings before continuing a long or expensive run. Dynamic workflows in Copilot CLI and the Copilot app (2026-10-01) · Oct 2026 · source · release history
- Supports parallel sub-agent execution within a dynamic workflow, enabling tasks like reviewing many pull-request files or sweeping a large codebase across directories simultaneously. Dynamic workflows in Copilot CLI and the Copilot app (2026-10-01) · Oct 2026 · source · release history
- Includes built-in Copilot authoring guidance so practitioners can ask Copilot to write a dynamic workflow entirely for them, or use 'What dynamic workflows are available?' to discover existing ones. Dynamic workflows in Copilot CLI and the Copilot app (2026-10-01) · Oct 2026 · source · release history
docs
- About GitHub Copilot Understand how GitHub Copilot helps you ship software faster, how it works, and how to get access. About GitHub Copilot agents Copilot agents use context and tools to plan and complete tasks. You can choose where and how you work with them. seen Oct 2026 · source
-
These articles provide how-to information for using Copilot cloud agent. For an overview of Copilot cloud agent, see GitHub Copilot on
GitHub.comseen Oct 2026 · source
example
-
Run a Copilot cloud task from inside your JetBrains IDE using the Air plugin.
1. Install the Air plugin in your JetBrains IDE. 2. Open the Air panel and select 'Cloud' from the environment selector. 3.GitHub Copilot is now available in JetBrains Air (2026-11-03) · Nov 2026 · source -
Start a cloud coding task in the browser without touching your local environment.
1. Open JetBrains Air in your browser. 2. Go to Settings > VCS Providers and connect your GitHub account. 3. Create a new task, choose your repository and remote branch. 4.GitHub Copilot is now available in JetBrains Air (2026-11-03) · Nov 2026 · source -
Plan a cross-repository API migration by finding all callers and implementations of the old API before writing any code.
/research Identify all repositories still calling the old payment API and list the changes each service needs to migrate.GitHub intelligence puts your code, context, and history to work (2026-10-28) · Oct 2026 · source -
Trace retry behavior scattered across a payments service, shared library, and background workers before making changes.
/research How do these components retry failed charges, and where could retries overlap?GitHub intelligence puts your code, context, and history to work (2026-10-28) · Oct 2026 · source -
Have Copilot author a reusable release-check workflow that pauses for human review before resuming.
Ask Copilot: 'Create a dynamic workflow that runs release checks, asks one agent to assess failures, and pauses at a checkpoint for me to review before resuming.'Dynamic workflows in Copilot CLI and the Copilot app (2026-10-01) · Oct 2026 · source -
Turn on experimental features mid-session and discover existing dynamic workflows without restarting the CLI.
/experimental on What dynamic workflows are available?Dynamic workflows in Copilot CLI and the Copilot app (2026-10-01) · Oct 2026 · source
Enterprise Billing Configuration shipped Allows administrators to set up, manage, and monitor per-user budgets with expiration controls for the cyber tool.
Also counts toward: REST API, Web management console
release 17 total
-
Look up which cost center a user, organization, repository, or enterprise team belongs to by passing the resource type and name to a new REST API endpoint — the response includes the cost center's ID and name, and returns an empty
membershipsarray when no cost center matches.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Look up a resource’s cost center with the GitHub REST API (2026-11-03) · Nov 2026 · source · release history - Code completion and next edit suggestions remain available even when the enterprise budget is exhausted, while Copilot Chat, Copilot code review, and Copilot in the cloud require available budget. GitHub Enterprise now includes access to GitHub Copilot (2026-10-28) · Oct 2026 · source · release history
- Adds a Scope menu to narrow the budget list to a single scope, such as organizations or cost centers. Search and filter for budgets now available (2026-10-13) · Oct 2026 · source · release history
-
Adds Choose how members with a Copilot license are billed setting under organization
Copilot -> Policies, with options Member (default, bills member's own entitlement) and Organization (bills the repository-owning org via AI Credits paid usage, with optional budget).︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Copilot code review: New organization billing options and controls (2026-10-08) · Oct 2026 · source · release history - Enables GitHub Team customers to start self-serve trials of GitHub Advanced Security, covering GitHub Code Security and GitHub Secret Protection, from the organization Overview page, Billing and licensing > Licensing page, or the Risk Assessment completion page.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub Advanced Security trials for GitHub Team (2026-09-30) · Sep 2026 · source · release history
- Enables organization owners, enterprise owners, and billing managers to approve, adjust, or deny budget requests — setting a new credit amount and immediately restoring access — without leaving settings. Copilot budget increase requests are generally available (2026-09-16) · Sep 2026 · source · release history
example
-
Switch Copilot code review billing to the organization cost center so member quotas are never consumed or exhausted.
In your organization settings, go to Copilot -> Policies, locate 'Choose how members with a Copilot license are billed', and select 'Organization'.Copilot code review: New organization billing options and controls (2026-10-08) · Oct 2026 · source -
Start a GitHub Advanced Security trial directly from your organization's billing settings without contacting sales.
In your GitHub organization, go to Settings > Billing and licensing > Licensing, then select 'Start trial' under GitHub Advanced Security.GitHub Advanced Security trials for GitHub Team (2026-09-30) · Sep 2026 · source -
Review and approve a member's Copilot budget increase request as an org owner so they regain AI credit access immediately.
In your organization's Settings, go to Billing > Requests from members, find the pending Copilot budget request, set a new amount, and select 'Approve and increase'.Copilot budget increase requests are generally available (2026-09-16) · Sep 2026 · source -
Opt in to the refreshed PR listing page and switch back to the classic view if needed.
1. Navigate to the pull requests tab of any repository. 2. Click the 'Preview' badge at the top of the page to enter the refreshed experience. 3.Refreshed repository pull requests page in public preview (2026-09-10) · Sep 2026 · source
Enterprise Credential Management shipped Provides administrators with bulk revocation and deauthorization capabilities for specific credential types across the enterprise or organization.
Also counts toward: REST API, Web management console
release 19 total
-
Adds a
telemetryproperty tomanaged-settings.jsonfor enterprise-managed Copilot settings to enable OTel export and specify the receiving endpoint, with prompt/response content excluded by default.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄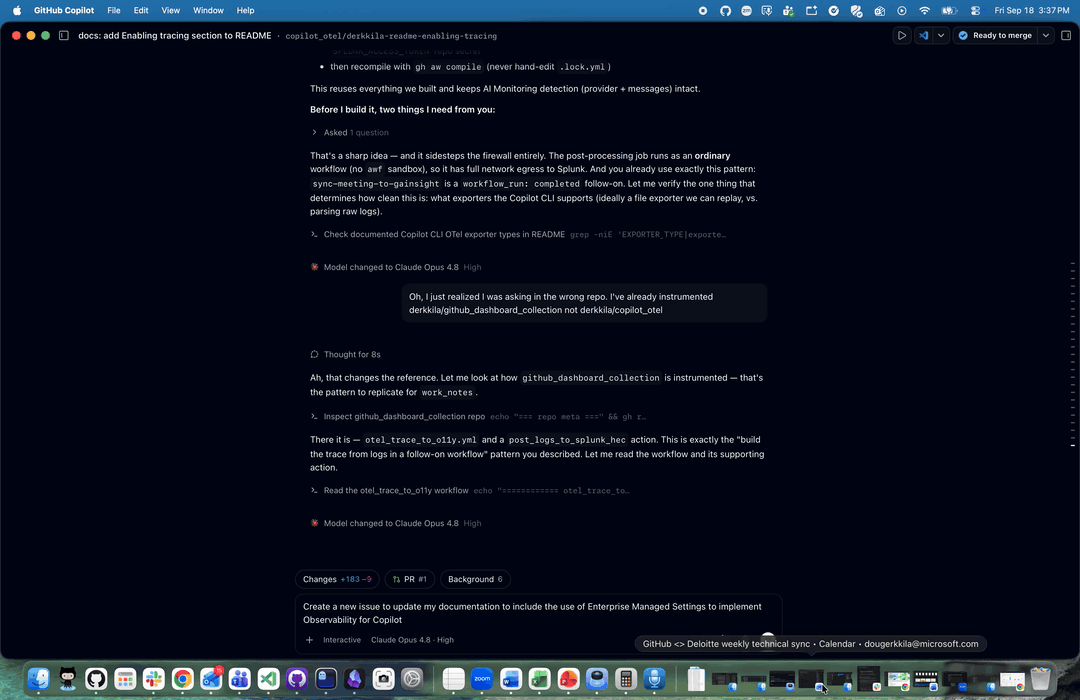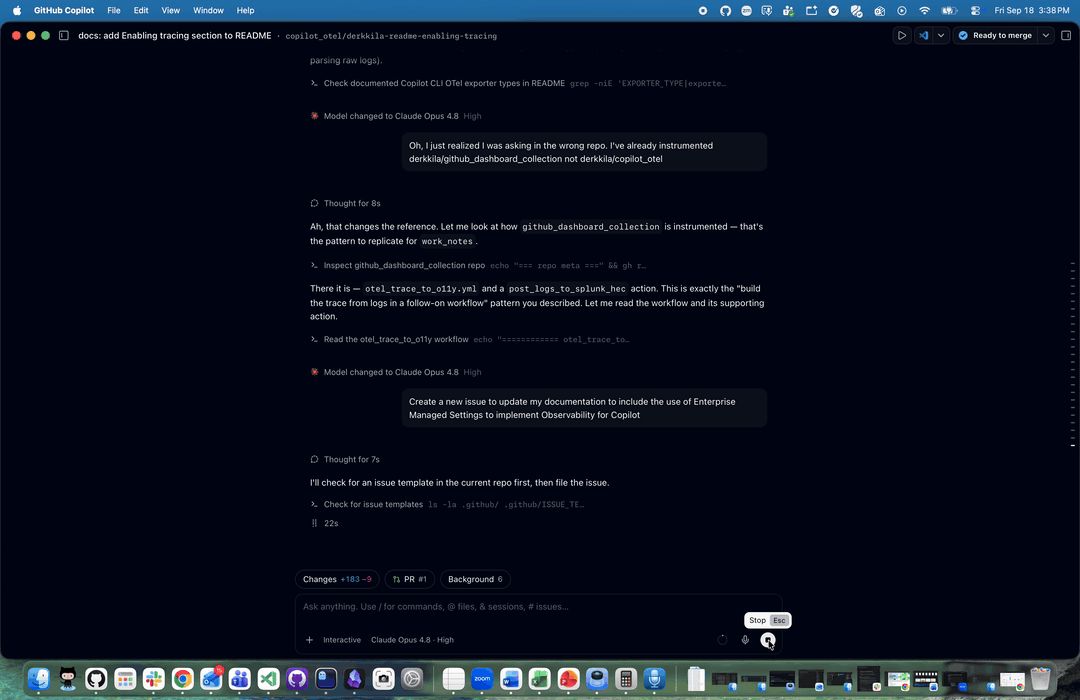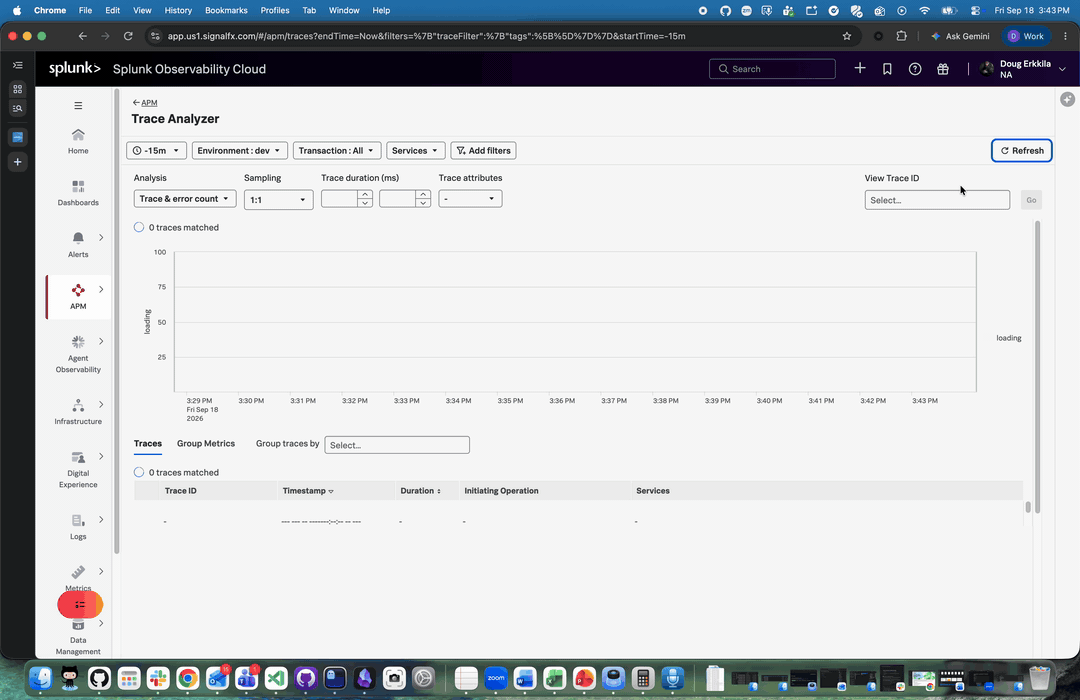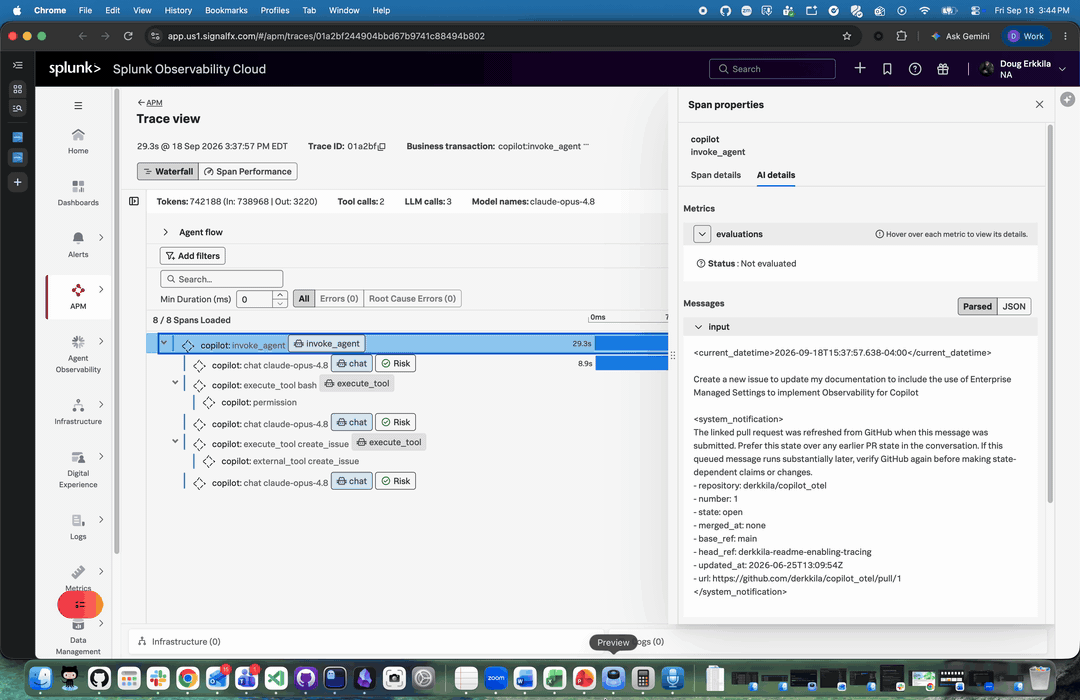 OpenTelemetry in the GitHub Copilot app (2026-09-23) · Sep 2026
· source
· release history
- Surfaces credential metadata in the inventory including owners, scopes and permissions, creation and expiration dates, last-used dates, and target organizations or repositories. GitHub Enterprise adds credential inventory exports (2026-09-21) · Sep 2026 · source · release history
- Adds new paginated REST API endpoints to programmatically retrieve the complete enterprise credential inventory for reporting and automation. GitHub Enterprise adds credential inventory exports (2026-09-21) · Sep 2026 · source · release history
- Adds a new View enterprise credentials fine-grained permission that grants members access to the enterprise credential inventory alongside enterprise owners.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub Enterprise adds credential inventory exports (2026-09-21) · Sep 2026 · source · release history
- Adds an Export CSV option in enterprise Settings -> Authentication Security -> Credentials to download the full credential inventory. GitHub Enterprise adds credential inventory exports (2026-09-21) · Sep 2026 · source · release history
- Covers SSH keys, classic and fine-grained personal access tokens, OAuth App access tokens, and GitHub App user-to-server and installation tokens in the exported inventory. GitHub Enterprise adds credential inventory exports (2026-09-21) · Sep 2026 · source · release history
example
-
Enable OTel export for all developers in your enterprise so agent sessions flow into your existing monitoring stack without per-developer configuration.
{ "telemetry": { "endpoint": "https://otel-collector.example.com" } }OpenTelemetry in the GitHub Copilot app (2026-09-23) · Sep 2026 · source -
Export a one-off CSV snapshot of all enterprise credentials for offline review or audit when you don't need automation.
In your enterprise, go to Settings -> Authentication Security -> Credentials and click 'Export CSV' next to the 'Overview' section.GitHub Enterprise adds credential inventory exports (2026-09-21) · Sep 2026 · source
Advanced Model Controls shipped Provides granular control over model behavior, including effort levels for reasoning depth and complementary 'second opinion' modes.
release 13 total
-
Choose an effort level — Fusion Standard, Fusion High, or Fusion Max — to control whether Copilot Fusion prioritizes versatile, capable, or the most capable models for a given task.
Route and orchestrate models with GitHub Copilot Fusion (2026-10-28) · Oct 2026
· source
· release history
- Adds per-stage reasoning-effort tuning to HydraFusion orchestration, using medium effort for initial drafts and high effort for review steps. HydraFusion updates and new Max option (2026-10-14) · Oct 2026 · source · release history
-
Adds taint flow models for
boost::asio::ip::basic_resolver::resolve, flow summaries forBloombergLP::bdlbb::Blob, and flow summaries for thegoogle::protobuf::MessageLiteC++ API, improving C/C++ taint tracking. CodeQL 2.27.1 adds C and C++ query and Kotlin 2.4.20 support (2026-09-25) · Sep 2026 · source · release history -
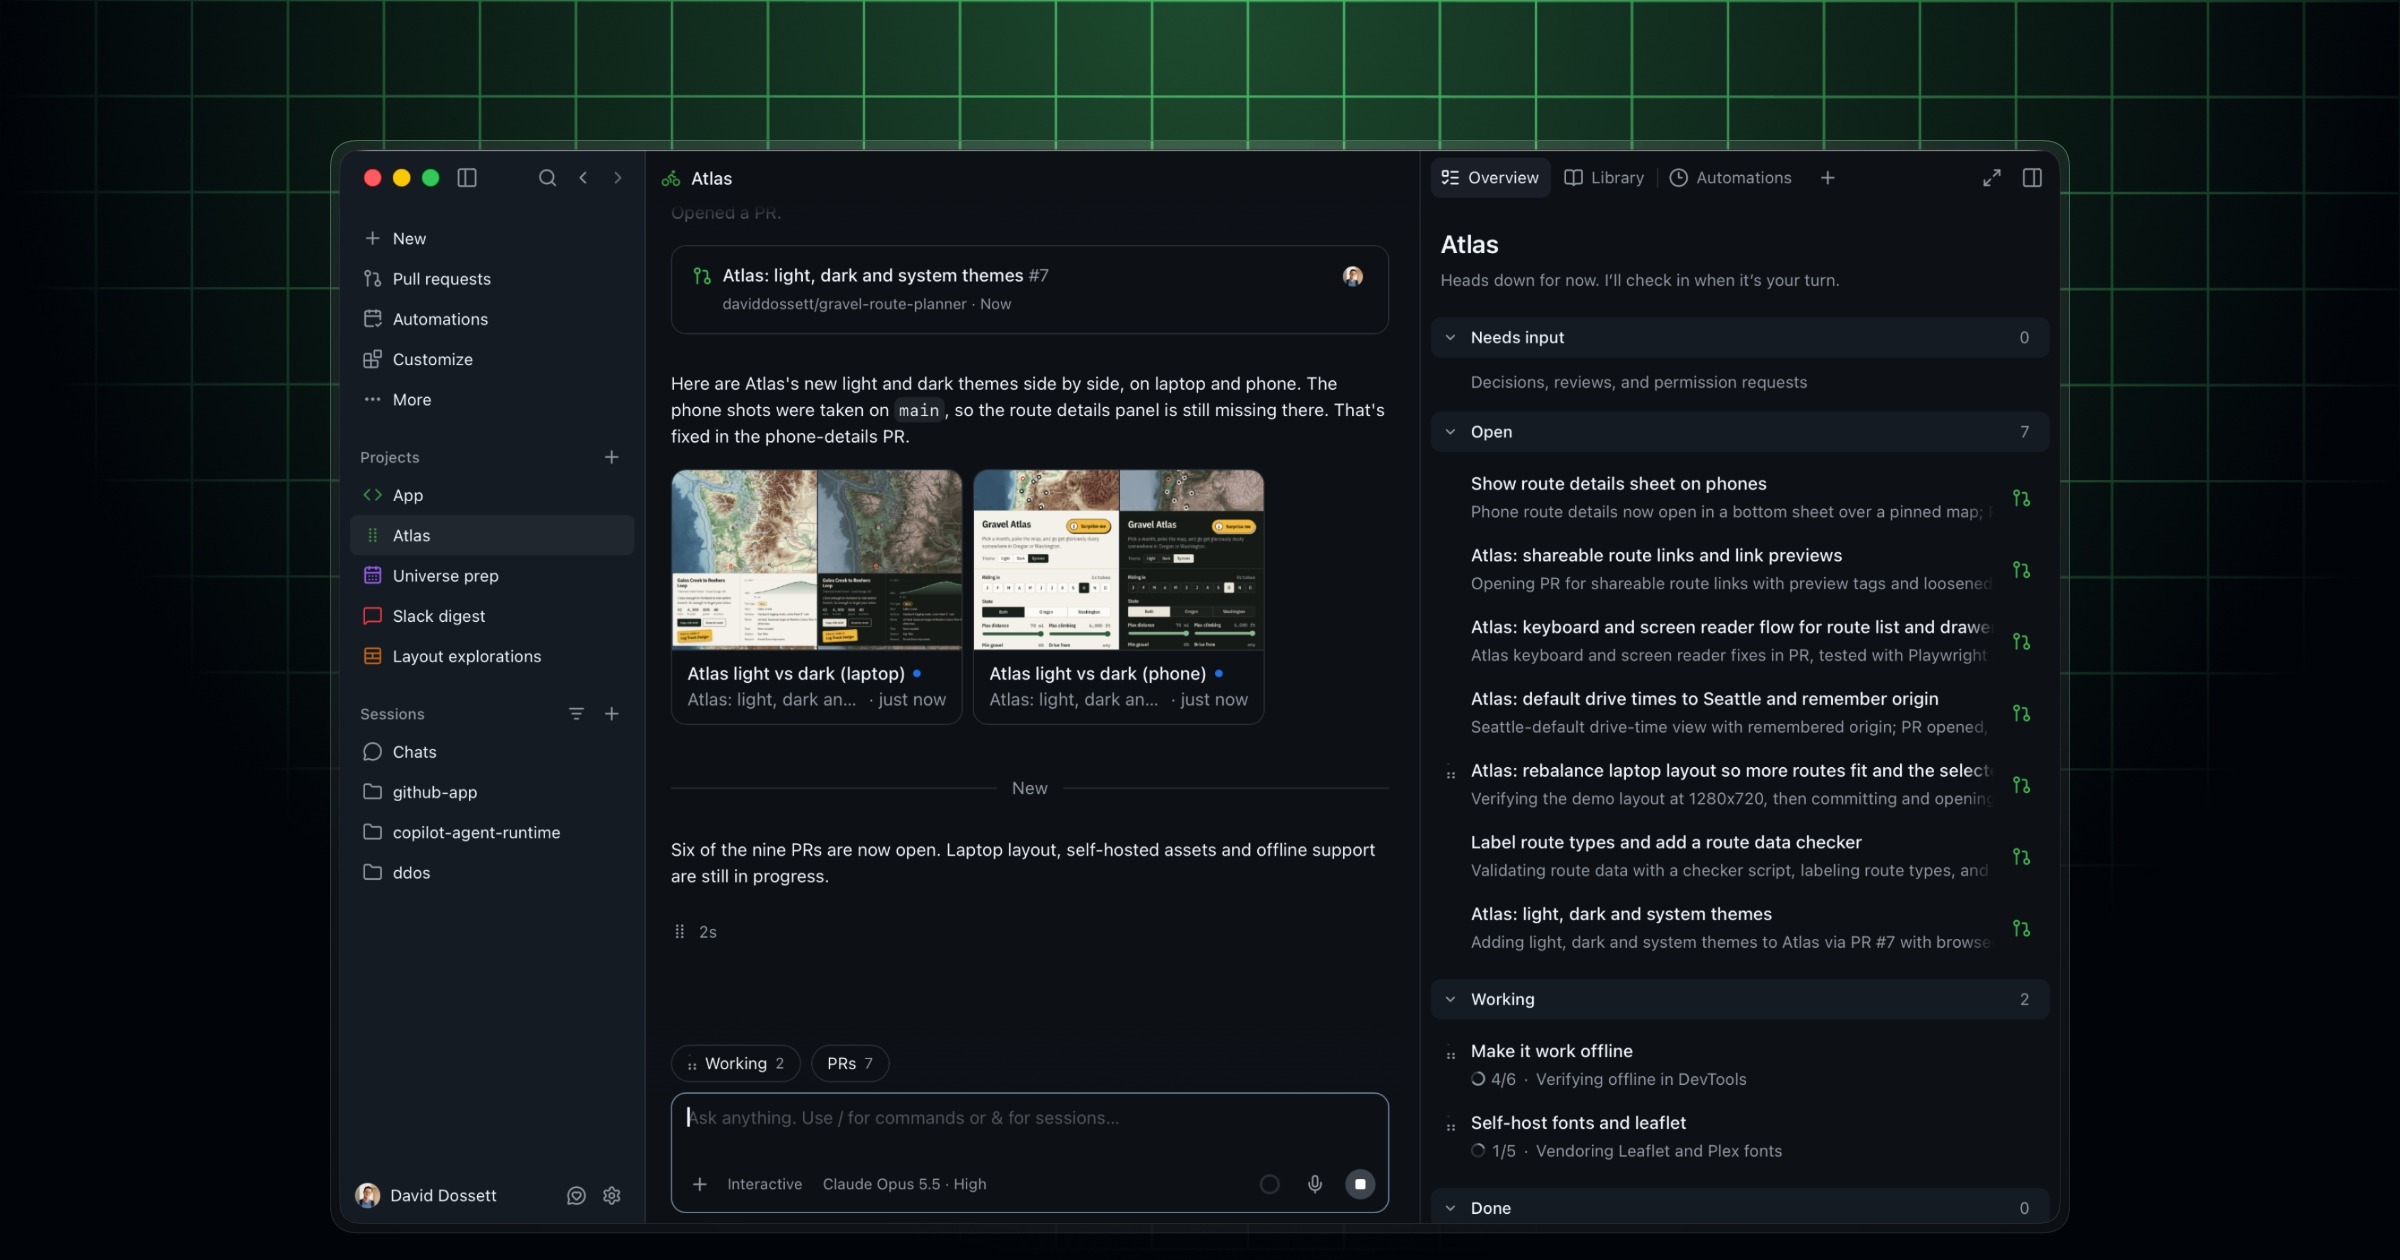
Adds
efficiency,balance, andintelligencetiers to auto model selection, letting users control how Copilot weighs cost, quality, and response time; rolling out in VS Code, Copilot CLI, and the Copilot app.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub Copilot weekly releases — September 14 (2026-09-18) · Sep 2026
· source
· release history
- Adds Enforce for repository and organization owners option to the Enforcement dropdown in security configurations, blocking organization administrators from overriding enterprise-level GitHub Advanced Security settings.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enforce GitHub Advanced Security configurations (2026-09-15) · Sep 2026 · source · release history
- Copilot-powered search across all portal content is available without sign-in. New customer portal help.github.com (2026-09-08) · Sep 2026 · source · release history
example 7 total
-
Select GPT-6.1 Sol for an agentic coding session in VS Code when you want fewer steps and lower token usage on multistep tasks.
In GitHub Copilot Chat (VS Code, JetBrains, or any supported IDE), open the model picker dropdown and select 'GPT-6.1 Sol', then issue your agentic coding prompt as normal.GPT-6.1 Sol in GitHub Copilot (2026-09-29) · Sep 2026 · source -
Select Claude Sonnet 5.5 for an agentic coding task in VS Code to take advantage of its faster, lower-token execution on well-scoped feature work.
In GitHub Copilot (VS Code, JetBrains, or github.com), open the model picker and select 'Claude Sonnet 5.5', then submit your Copilot Chat or coding agent prompt as normal.Claude Sonnet 5.5 in GitHub Copilot (2026-09-28) · Sep 2026 · source -
Switch to GPT-6 Luna in Copilot CLI for fast, low-cost inline suggestions during a code review session.
In Copilot CLI, open the model picker and select `GPT-6 Luna` before running your query.OpenAI’s GPT-6 Sol and GPT-6 Luna now available (2026-09-22) · Sep 2026 · source -
Prioritise response quality over cost for a high-stakes investigation by switching auto model selection to the
intelligencetier.In VS Code (or Copilot CLI / Copilot app): open Copilot settings > Auto model selection > set tier to `intelligence` to have Copilot pick the highest-quality available model for each request.GitHub Copilot weekly releases — September 14 (2026-09-18) · Sep 2026 · source -
Get a second opinion from a complementary model on the current agent session to catch missed edge cases before merging.
/rubber-duckGitHub Copilot in VS Code, August 2026 releases (2026-08-31) · Aug 2026 · source -
Keep Lite as your org's code review default before the September 28th cutover, so automated reviews don't silently become more expensive.
Go to your organization's Copilot settings on github.com > Code review > Review effort level, then change the value from 'Default' to explicitly select 'Lite' before September 28th, 2026.Upcoming changes to GitHub Copilot policies and billing (2026-08-28) · Aug 2026 · source
Security Advisory Comments shipped Allows posting, editing, listing, and retrieving comments on repository security advisories, including confidential comments with permission-gated access and audit logging.
release 15 total
-
Adds
GETendpoint to retrieve a single comment on a repository security advisory. Repository security advisory comments API in public preview (2026-10-02) · Oct 2026 · source · release history -
Adds
GETendpoint to list comments on a repository security advisory, with optional filtering by last-updated time.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Repository security advisory comments API in public preview (2026-10-02) · Oct 2026 · source · release history -
Adds
comments_countfield to individual repository advisory responses and includes this count in global advisory list responses for linked repositories. Repository security advisory comments API in public preview (2026-10-02) · Oct 2026 · source · release history -
Global advisory responses now include the
comments_countfrom their linked repository advisory. Repository security advisory comments API in public preview (2026-10-02) · Oct 2026 · source · release history - Adds Confidential option when posting comments on repository security advisories to restrict visibility to users with write access Confidential comments on repository security advisories (2026-10-02) · Oct 2026 · source · release history
-
Adds
POST /repos/{owner}/{repo}/advisories/{advisory_number}/commentsendpoint to add new comments to repository security advisories, including those from private reports. Repository security advisory comments API in public preview (2026-10-02) · Oct 2026 · source · release history
example
-
Check which open advisories already have discussion before pulling full comment threads — useful when triaging a backlog.
curl -H 'Authorization: Bearer <token>' \ -H 'Accept: application/vnd.github+json' \ 'https://api.github.com/repos/<owner>/<repo>/security-advisories' \ | jq '[.[] | select(.comments_count > 0) |…Repository security advisory comments API in public preview (2026-10-02) · Oct 2026 · source -
Automatically post a triage note to a security advisory when your pipeline finishes analysis — keeping advisory discussion out of the web UI and in your toolchain.
curl -X POST \ -H 'Authorization: Bearer <token>' \ -H 'Accept: application/vnd.github+json' \ https://api.github.com/repos/<owner>/<repo>/security-advisories/<ghsa_id>/comments \ -d '{"body":…Repository security advisory comments API in public preview (2026-10-02) · Oct 2026 · source -
Post a confidential internal note on an advisory — e.g. to record investigation details without exposing them to the reporter or invited collaborators.
In the security advisory, type your comment, select 'Confidential' below the comment box, then click Submit.Confidential comments on repository security advisories (2026-10-02) · Oct 2026 · source -
Post a maintenance-only note on an advisory without alerting the reporter
Steps: Navigate to the security advisory timeline. Click 'Add comment'. Toggle 'Confidential' before posting.Confidential comments on repository security advisories (2026-10-02) · Oct 2026 · source -
Export all advisory comments updated since a given date for an audit trail or migration to another system.
curl -H 'Authorization: Bearer <token>' \ -H 'Accept: application/vnd.github+json' \ 'https://api.github.com/repos/<owner>/<repo>/security-advisories/<ghsa_id>/comments?since=2026-01-01T00:00:00Z'Repository security advisory comments API in public preview (2026-10-02) · Oct 2026 · source
Computer Use Automation shipped Allows Copilot to interact with desktop applications by controlling mouse, keyboard, and screen — including GUI-only and legacy software — via a managed settings panel with per-app approval controls.
release 11 total
-
Enable computer use for desktop app automation by going to Settings > Computer Use and turning on Enable Computer Use; grant Accessibility and Screen Recording permissions on macOS.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
 GitHub Copilot app, Universe releases (2026-10-28) · Oct 2026
· source
· release history
- GitHub Copilot app now supports computer use (public preview on macOS and Windows), letting Copilot read content, click controls, enter text, and navigate across desktop apps — including those with no API, CLI, or MCP integration. GitHub Copilot app, Universe releases (2026-10-28) · Oct 2026 · source · release history
-
Enable computer use so Copilot can interact with desktop apps (clicking controls, editing text) by enabling
chat.agentHost.computerUse.enabledin VS Code Settings, restarting VS Code, then running/computer onin a Copilot session.
GitHub Copilot in VS Code, Universe releases (2026-10-28) · Oct 2026
· source
· release history
-
/computer on,/computer show, and/computer offsubcommands in GitHub Copilot CLI to control computer-use capability GitHub Copilot can now interact with desktop apps with computer use (2026-10-01) · Oct 2026 · source · release history - Organization-managed setting to disable the computer-use feature GitHub Copilot can now interact with desktop apps with computer use (2026-10-01) · Oct 2026 · source · release history
- Adds a Computer Use settings panel in the GitHub Copilot app (Settings > Computer Use > Enable Computer Use) with per-app approval controls and the ability to review or reset always-allowed apps. GitHub Copilot can now interact with desktop apps with computer use (2026-10-01) · Oct 2026 · source · release history
docs
- About computer use in GitHub Copilot Copilot can interact with desktop applications to automate tasks that cannot be completed with a more direct tool. docs update · Oct 2026 · source
example 7 total
-
Let Copilot interact with desktop apps — filling forms, clicking UI controls — by enabling computer use in VS Code settings and activating it in the current session.
# 1. In VS Code Settings, enable chat.agentHost.computerUse.enabled and restart VS Code # 2. In a Copilot session panel, run: /computer onGitHub Copilot in VS Code, Universe releases (2026-10-28) · Oct 2026 · source -
Enable Copilot to control desktop apps (such as expense-report workflows) on a managed macOS machine without requiring an API or MCP integration.
In the GitHub Copilot app, go to Settings > Computer Use and turn on 'Enable Computer Use'. When prompted by macOS, grant Accessibility and Screen Recording permissions.GitHub Copilot app, Universe releases (2026-10-28) · Oct 2026 · source -
Check whether computer use is active in the current Copilot CLI session, or turn it off after finishing an automated workflow.
/computer show /computer offGitHub Copilot can now interact with desktop apps with computer use (2026-10-01) · Oct 2026 · source -
Enable and check status of computer use in CLI sessions to automate desktop workflows.
/computer on /computer showGitHub Copilot can now interact with desktop apps with computer use (2026-10-01) · Oct 2026 · source -
Turn on computer use via the app UI to allow Copilot to interact with desktop apps.
In the GitHub Copilot app, open Settings > Computer Use and turn on Enable Computer Use.GitHub Copilot can now interact with desktop apps with computer use (2026-10-01) · Oct 2026 · source -
Enable Computer Use from the GitHub Copilot app UI on macOS or Windows when you prefer not to use the CLI.
Open the GitHub Copilot app > Settings > Computer Use > turn on 'Enable Computer Use'. On macOS, follow the prompted steps to grant Accessibility and Screen Recording permissions.GitHub Copilot can now interact with desktop apps with computer use (2026-10-01) · Oct 2026 · source
Unified Agent Experience Policy shipped Allows administrators to define and enforce policy configurations for the unified agent experience across different platforms.
release 11 total
- Organization administrators must enable the 'Allow use of Copilot cloud agent billed to the organization' policy for shared automations to run in organization-owned repositories. Build shared workflows for your team with Copilot Automations (2026-10-28) · Oct 2026 · source · release history
- Adds a Copilot metrics industry comparison policy — opt in from the dashboard or centrally from enterprise or organization Copilot policies — that controls both data contribution and visibility with a single toggle. Industry comparisons in the Copilot impact dashboard (2026-10-22) · Oct 2026 · source · release history
- Enables peer group filtering by company size (1–999, 1,000–4,999, or 5,000+ employees) and one of ten industries, with automatic widening to all industries when a selected industry's peer group is too small. Industry comparisons in the Copilot impact dashboard (2026-10-22) · Oct 2026 · source · release history
- Enables coding agents to avoid recommending packages that violate an organization's license policy via the new package compliance check endpoint. Open source license compliance generally available (2026-10-16) · Oct 2026 · source · release history
- Integrates with Dependabot so that version-update PRs for onboarded workflows automatically regenerate the matching lockfile entry in the same pull request. GitHub Actions workflow lockfiles in public preview (2026-10-14) · Oct 2026 · source · release history
- Introduces the Require lockfile policy (public preview) allowing Enterprise, organization, and repository administrators to mandate lockfile use across their scope. GitHub Actions workflow lockfiles in public preview (2026-10-14) · Oct 2026 · source · release history
docs
- Made for organizations and enterprises, this plan offers centralized management and Copilot policy control for organization members. seen Oct 2026 · source
example 7 total
-
Opt your enterprise into industry comparisons so leaders can benchmark agentic Copilot adoption against peers of the same size and sector.
In the Copilot impact dashboard, go to the 'Industry comparison' section and enable the Copilot metrics industry comparison policy.Industry comparisons in the Copilot impact dashboard (2026-10-22) · Oct 2026 · source -
Ensure a freshly pushed policy change takes effect before any Copilot client starts — useful after revoking access or changing sandbox rules in a compliance-sensitive environment.
forceRemoteSettingsRefresh: trueEnterprise managed settings enforcement updates (2026-10-13) · Oct 2026 · source -
Check whether computer use is active in the current Copilot CLI session, or turn it off after finishing an automated workflow.
/computer show /computer offGitHub Copilot can now interact with desktop apps with computer use (2026-10-01) · Oct 2026 · source -
Prevent any new generally available Copilot features from rolling out to users automatically until an administrator explicitly approves them.
In the GitHub enterprise admin console, go to AI Controls > Copilot > 'Default policy for new features' and select 'Disabled'.Default Enablement of Copilot features for Copilot Business and Enterprise (2026-09-25) · Sep 2026 · source -
Prevent all future GA Copilot features from being silently enabled for your enterprise users until an admin explicitly approves them.
In GitHub, go to your enterprise settings > AI Controls > Copilot > Features & clients (https://github.com/enterprises/YOUR-ENTERPRISE-SLUG/ai-controls/copilot/features), then under 'Default policy…Default Enablement of Copilot Features for Copilot Business and Enterprise (2026-09-25) · Sep 2026 · source -
Delegate Copilot feature rollout decisions to individual organization admins rather than setting a single enterprise-wide default.
In the GitHub enterprise admin console, go to AI Controls > Copilot > 'Default policy for new features' and select 'Let organizations decide'.Default Enablement of Copilot features for Copilot Business and Enterprise (2026-09-25) · Sep 2026 · source
Integrated Chat Platform Access shipped Provides mechanisms to trigger and manage Copilot agent sessions directly within Microsoft Teams and Slack channels.
Also counts toward: Built-in AI assistant
release 15 total
- Consolidates the former GitHub notifications Teams app and Copilot capabilities into a single unified GitHub app for Microsoft Teams. Turn notifications into code with GitHub Copilot in Teams (2026-10-23) · Oct 2026 · source · release history
-
Adds
@githubmention support in Microsoft Teams channels, group chats, and private chats to trigger Copilot actions — such as investigating an issue, fixing a bug, and opening a pull request — directly from a notification.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Turn notifications into code with GitHub Copilot in Teams (2026-10-23) · Oct 2026 · source · release history - The legacy GitHub app in Microsoft Teams will be renamed GitHub (deprecated) and retired on November 16; users must install the consolidated GitHub app to retain Copilot in Teams functionality. Turn notifications into code with GitHub Copilot in Teams (2026-10-23) · Oct 2026 · source · release history
- Uses shared Slack messages and threads as context so Copilot can reference discussions without manual copy-paste. Multi-repo support and other improvements for GitHub Copilot in Slack and Microsoft Teams (2026-10-16) · Oct 2026 · source · release history
- Adds support for shared Slack messages and threads as context for @GitHub, reducing the need to copy and paste discussion details. Multi-repository support and other improvements for GitHub in Slack and Teams (2026-10-16) · Oct 2026 · source · release history
-
Allows
@GitHubto be mentioned anywhere in a message, not just at the beginning. Multi-repo support and other improvements for GitHub Copilot in Slack and Microsoft Teams (2026-10-16) · Oct 2026 · source · release history
example
-
Get a cross-repo PR status summary without leaving Slack — useful at the start of a team standup.
@GitHub Show me all my open pull requests across repositories and highlight which ones need my attention.Multi-repo support and other improvements for GitHub Copilot in Slack and Microsoft Teams (2026-10-16) · Oct 2026 · source -
Investigate a bug that touches multiple services by asking Copilot in the context of an existing Slack thread about the incident.
@GitHub Help me investigate an issue that spans our frontend and backend repositories.Multi-repo support and other improvements for GitHub Copilot in Slack and Microsoft Teams (2026-10-16) · Oct 2026 · source -
Triage a bug across frontend and backend repos in one Slack thread without opening GitHub.
Steps: 1. In any Slack thread, type: '@GitHub Investigate this issue using the code in our frontend and backend repositories.' 2.Multi-repository support and other improvements for GitHub in Slack and Teams (2026-10-16) · Oct 2026 · source -
Give Copilot richer context in a Teams thread by forwarding a message from another channel before asking it to draft an issue.
In Microsoft Teams, forward the relevant message into the current thread, then mention @GitHub and ask it to create an issue — Copilot will use the forwarded-message context and thread history in its…Updates to GitHub Copilot for Slack and Microsoft Teams (2026-09-25) · Sep 2026 · source
Dynamic Model Orchestration shipped Provides access to models that dynamically orchestrate multiple AI providers using Single, Cascade, or Critique execution patterns to balance quality, cost, and latency per task.
Also counts toward: Command-line interface
release 14 total
- Route model selection automatically per workflow using a model router that optimizes for task type and difficulty. GitHub Agentic Workflows generally available (2026-10-28) · Oct 2026 · source · release history
-
Select Copilot Fusion in the model picker to let Copilot automatically route and orchestrate which models handle each prompt, choosing from Single (one model), Cascade (draft-then-escalate), or Critique (draft-review-revise) workflows without manual model switching.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Route and orchestrate models with GitHub Copilot Fusion (2026-10-28) · Oct 2026
· source
· release history
- Expands the HydraFusion model pool to include Claude Opus 5.5, GPT-6 Astra, GPT-6.1 Sol, and GPT-6 Luna. HydraFusion updates and new Max option (2026-10-14) · Oct 2026 · source · release history
- Introduces HydraFusion Max, a new model-orchestration option tuned for frontier capability on demanding tasks with higher reasoning effort and token-efficiency orchestration, available in VS Code, GitHub Copilot app, and GitHub Copilot CLI.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ HydraFusion updates and new Max option (2026-10-14) · Oct 2026 · source · release history
-
Adds
HydraFusionmodel-picker option (research preview) to automatically select models and workflows for coding tasks.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub Copilot in VS Code, September 2026 releases (2026-10-01) · Oct 2026 · source · release history - Adds HydraFusion to VS Code (version 1.140 or later, including VS Code Insiders) and the GitHub Copilot app, expanding beyond Copilot CLI. HydraFusion in VS Code and the GitHub Copilot app (2026-09-30) · Sep 2026 · source · release history
example
-
When you want Copilot to handle model selection automatically for a demanding refactor or architecture task without manually switching models.
Open the model picker in Visual Studio Code or JetBrains, select 'Copilot Fusion', then choose 'Fusion Max' as the effort level to apply the most capable models to complex reasoning tasks.Route and orchestrate models with GitHub Copilot Fusion (2026-10-28) · Oct 2026 · source -
Turn on HydraFusion in the GitHub Copilot app to access multi-model orchestration on mobile or desktop outside VS Code.
In the GitHub Copilot app: go to Settings, search for 'HydraFusion', turn it on, then select HydraFusion from the model picker.HydraFusion in VS Code and the GitHub Copilot app (2026-09-30) · Sep 2026 · source -
Enable HydraFusion in VS Code when it does not appear in the model picker — useful for early adopters or orgs where the feature is not yet visible by default.
chat.copilot.hydraFusion.enabledHydraFusion in VS Code and the GitHub Copilot app (2026-09-30) · Sep 2026 · source -
Route a high-latency coding task through the best available model automatically, instead of manually choosing between local and cloud models.
In Copilot CLI, open the model selector and choose `HydraFusion` (listed under `/experimental`) — submit your task as normal and HydraFusion selects the local, cloud, or compound workflow based on…GitHub Copilot weekly releases — September 7 (2026-09-10) · Sep 2026 · source
Agent Execution Sandboxing shipped Runs agent tasks in a secure, isolated cloud environment to prevent side effects in the user's local machine.
Also counts toward: Built-in AI assistant
release 16 total
-
Run Copilot cloud tasks in isolated Docker containers on fresh virtual machines through Air Teams, billed to your existing Copilot plan rather than JetBrains AI credits.
GitHub Copilot is now available in JetBrains Air (2026-11-03) · Nov 2026
· source
· release history
- Agents run with read-only permissions by default, execute inside a sandboxed container behind the Agent Workflow Firewall, and have all proposed changes scanned by a dedicated threat detection job before they are applied. GitHub Agentic Workflows generally available (2026-10-28) · Oct 2026 · source · release history
-
Organizations using per-host network allowlists for GitHub Actions blob storage must add
productionresultssa30throughproductionresultssa49andproductionresultssa100throughproductionresultssa199(all under.blob.core.windows.net) or job summaries and logs will be interrupted. Meta API endpoints updated for Actions blob storage (2026-10-22) · Oct 2026 · source · release history -
Adds
productionresultssa30.blob.core.windows.netthroughproductionresultssa49.blob.core.windows.netandproductionresultssa100.blob.core.windows.netthroughproductionresultssa199.blob.core.windows.netas new GitHub Actions blob storage hosts, retrievable via the REST meta data API.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Meta API endpoints updated for Actions blob storage (2026-10-22) · Oct 2026 · source · release history - Supports sandboxing of local MCP and language servers where supported. Local sandboxing for GitHub Copilot now generally available (2026-10-07) · Oct 2026 · source · release history
- Adds local sandboxing for GitHub Copilot (powered by Microsoft eXecution Container, MXC) in GitHub Copilot CLI, the GitHub Copilot app, and VS Code Agent Host sessions, restricting agentic tool and command access to the filesystem, network, and credentials.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Local sandboxing for GitHub Copilot now generally available (2026-10-07) · Oct 2026 · source · release history
example
-
Disable the built-in GitHub MCP Server to avoid conflicts with a custom MCP configuration while keeping your other manually configured MCP servers active.
In the Copilot tool window, open MCP tool settings, locate the labeled 'built-in GitHub MCP Server' entry, and toggle it off. Manually configured MCP servers remain unaffected.New features and improvements in Copilot for JetBrains (2026-09-23) · Sep 2026 · source
User Experience Customization shipped Offers controls to customize the look, feel, and input methods of the agent interface, including layout, dictation, and editor associations.
release 16 total
- The Copilot agent placeholder now highlights questions, edits, context, and commands to guide agent interactions. New controls and chat improvements in Copilot for JetBrains (2026-10-10) · Oct 2026 · source · release history
- A one-time reminder helps new users discover Chat, with a reworked sign-in page featuring a responsive layout, clearer headings, improved provider choices, a direct Copilot plans link, and cancellable browser-authorization progress. New controls and chat improvements in Copilot for JetBrains (2026-10-10) · Oct 2026 · source · release history
- Adds a Switch Account action to signed-in Copilot account controls, along with clearer labels, a simpler status display, and better navigation for long account lists. New controls and chat improvements in Copilot for JetBrains (2026-10-10) · Oct 2026 · source · release history
- User messages in chat now include actions to copy or edit their content. New controls and chat improvements in Copilot for JetBrains (2026-10-10) · Oct 2026 · source · release history
-
Enables use of separate GitHub accounts for a Copilot license and repository access in the Copilot app (e.g. enterprise-provided license paired with a personal repository account).
 GitHub Copilot weekly releases — October 5 (2026-10-09) · Oct 2026
· source
· release history
- Adds Open worktree cleanup in VS Code chat to surface disk usage of inactive session worktrees and remove selected ones. GitHub Copilot weekly releases — October 5 (2026-10-09) · Oct 2026 · source · release history
example
-
Standardize Copilot review depth across all org-owned repositories in an enterprise, so teams without their own override inherit a consistent baseline.
As an enterprise administrator, go to your enterprise settings → Copilot → Code review, and set the enterprise-wide 'Default review effort' to Lite, Balanced, or GitHub default.More ways to request and configure Copilot code reviews (2026-09-23) · Sep 2026 · source
Agent Context and Environment Support shipped Allows agents to operate within specific project environments (Dev Containers) or external data sources (Sentry) to provide accurate code fixes and reviews.
release 11 total
-
Bring context from services such as Slack, Notion, and Microsoft Learn into agent sessions without an MCP server using Copilot connectors, available in preview from the Browse page on all Copilot plans.
GitHub Copilot in VS Code, Universe releases (2026-10-28) · Oct 2026
· source
· release history
- Adds Use Dev Container option in the Agents window to start agent sessions inside a project's Dev Container on local, SSH, Tunnel, and WSL hosts. GitHub Copilot in VS Code, September 2026 releases (2026-10-01) · Oct 2026 · source · release history
- Enables Dependabot jobs to target self-hosted runners or larger GitHub-hosted runners — useful for access to private package registries or specialized build environments. Repository custom runner settings for Dependabot (2026-09-29) · Sep 2026 · source · release history
- Repository-level runner settings are available for private and internal repositories on github.com; hidden for public repositories and not available on GitHub Enterprise Server. Repository custom runner settings for Dependabot (2026-09-29) · Sep 2026 · source · release history
-
Adds repository-level runner configuration for Dependabot version and security updates, letting admins choose Labeled runner or
Standard GitHub runnerunder Settings > Advanced Security > Dependency scanning > Dependabot version updates > Runner type.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Repository custom runner settings for Dependabot (2026-09-29) · Sep 2026 · source · release history -
Supports optional custom runner label and runner group when Labeled runner is selected; defaults to the
dependabotlabel if no label is specified. Repository custom runner settings for Dependabot (2026-09-29) · Sep 2026 · source · release history
example
-
Run an agent session inside your project's Dev Container so it has access to the exact toolchain and dependencies defined in your devcontainer config.
In the Agents window, open the menu for your local or remote folder and select 'Use Dev Container' to launch the agent session inside the configured container (works on SSH, Tunnel, and WSL hosts).GitHub Copilot in VS Code, September 2026 releases (2026-10-01) · Oct 2026 · source -
Route Dependabot jobs to a self-hosted runner with access to a private package registry by setting a custom runner label at the repository level.
1. Go to your repository on github.com. 2. Navigate to Settings > Advanced Security. 3. Under 'Dependency scanning', find 'Dependabot version updates' and click 'Runner type'. 4.Repository custom runner settings for Dependabot (2026-09-29) · Sep 2026 · source -
Run a Copilot agent against a project that requires specific runtimes or dependencies defined in a Dev Container, so the agent uses the same environment as local development.
In VS Code 1.138, open the Agents window > start or resume a session > Copilot automatically launches the local Dev Container (Docker must be running and a Dev Container configuration must exist in…GitHub Copilot weekly releases — September 14 (2026-09-18) · Sep 2026 · source -
When a Sentry alert fires in production, jump straight from the crash report into a fix workflow without leaving GitHub.
In the GitHub Copilot app: open the Sentry canvas > select a Sentry error report > review the stack trace and related context > ask Copilot to investigate the root cause > validate the proposed fix >…GitHub Copilot weekly releases — September 14 (2026-09-18) · Sep 2026 · source
Code Review UX and Workflow Improvements shipped Enhances the code review experience with prioritized findings, overview grouping, direct PR creation from agents, and efficient session management.
release 8 total
- In split view, new and deleted files now span both columns (full width), matching unified view behavior to reduce line wrapping. Pull requests: Saved whitespace preferences and improved split view (2026-10-22) · Oct 2026 · source · release history
-
Displays an active Hide whitespace filter badge beside All commits when whitespace is hidden, with an
Xto temporarily reveal whitespace without changing the saved preference. Pull requests: Saved whitespace preferences and improved split view (2026-10-22) · Oct 2026 · source · release history - Adds a persistent whitespace visibility preference under Settings → Whitespace changes with options Always show, Always hide, or Hide for this diff only, applied per user across all pull requests.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Pull requests: Saved whitespace preferences and improved split view (2026-10-22) · Oct 2026 · source · release history
- Adds pull request creation directly from Copilot, Claude, or Codex agent sessions in the Agents window, with title/description editing, draft and merge options. GitHub Copilot in VS Code, September 2026 releases (2026-10-01) · Oct 2026 · source · release history
-
Adds pull request creation directly from Agent Host sessions in the VS Code Agents window, including generated title and description, draft status selection, and agent-assisted creation.
GitHub Copilot weekly releases — September 14 (2026-09-18) · Sep 2026
· source
· release history
-
Adds titles to every Copilot code review comment for at-a-glance prioritization, reused in the overview issue list.
 Copilot code review: An improved review experience (2026-09-18) · Sep 2026
· source
· release history
example
-
Turn a bug-report notification into a pull request without leaving a Teams channel.
In the Teams channel where the bug notification appeared, type: @github fix the issue in <repo> and create a pull request, then follow the prompts to connect your GitHub account and select a…Turn notifications into code with GitHub Copilot in Teams (2026-10-23) · Oct 2026 · source -
Surface a summary of an open pull request — with links to its comments and files — without leaving Visual Studio.
1. Open GitHub Copilot Chat. 2. Select the Git agent. 3. In the Git Repository window, right-click the pull request and choose 'Attach as context'. 4.GitHub Copilot in Visual Studio — September update (2026-10-23) · Oct 2026 · source -
Set a personal whitespace preference that persists across all PRs so you never have to re-hide noisy formatting changes.
In a pull request, go to the 'Files changed' tab → open Settings → Whitespace changes → select 'Always hide'. Your preference is saved and applied to all future PRs automatically.Pull requests: Saved whitespace preferences and improved split view (2026-10-22) · Oct 2026 · source -
Temporarily reveal whitespace on a specific diff without losing your saved Always hide preference.
When reviewing a PR with whitespace hidden, locate the 'Hide whitespace' filter badge beside 'All commits' and click its X to show whitespace for the current diff only.Pull requests: Saved whitespace preferences and improved split view (2026-10-22) · Oct 2026 · source -
Get a cross-repo PR review queue from Slack to prioritise your review work each morning.
Steps: 1. In any Slack channel or DM, type: '@GitHub Show me all my open PRs across repositories and highlight which ones need my attention.' 2.Multi-repository support and other improvements for GitHub in Slack and Teams (2026-10-16) · Oct 2026 · source -
Quickly triage a Copilot review by checking which issues are still open, which were fixed, and which were newly surfaced in existing code — all from the overview comment without scrolling through inline threads.
In the pull request, open the Copilot overview comment > review findings grouped under 'Open', 'Resolved since last review', and 'Previously missed' > click the inline-comment link next to any…Copilot code review: An improved review experience (2026-09-18) · Sep 2026 · source
AI-Detected Secret Scanning shipped suggested Uses a purpose-built fine-tuned model to detect unstructured credentials and AI-detected secrets in repositories, available on GitHub Enterprise Server 3.23 and surfaced in Copilot CLI and Copilot App security review sessions.
Suggested capability: Static application security testing. This is our guess, not confirmed.
Also counts toward: Command-line interface
release 13 total
- Enterprise admins and enterprise security managers can enable public monitoring under enterprise security settings, included at no additional cost with an active GitHub Advanced Security or GitHub Secret Protection license. Public monitoring now available with data residency (2026-10-22) · Oct 2026 · source · release history
- Delivers secret scanning alerts encrypted directly to the enterprise dashboard, keeping data within the designated geography through tenant isolation.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Public monitoring now available with data residency (2026-10-22) · Oct 2026 · source · release history
-
Adds detection of
cloudsmith_api_key, generating alerts in public and private repositories. Secret scanning blocks Anthropic keys by default, adds Salesforce (2026-10-13) · Oct 2026 · source · release history -
Adds
salesforce_marketing_cloud_api_oauth2_tokendetection via a new Salesforce secret scanning partnership, automatically forwarding found secrets to Salesforce for revocation in public repositories.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Secret scanning blocks Anthropic keys by default, adds Salesforce (2026-10-13) · Oct 2026 · source · release history -
Adds detection of
anthropic_service_api_keyandanthropic_user_api_keysecret types, generating alerts in both public and private repositories. Secret scanning blocks Anthropic keys by default, adds Salesforce (2026-10-13) · Oct 2026 · source · release history - Brings AI-detected secret alerts to GitHub Enterprise Server 3.23 in public preview, included with existing GHSP and GHAS purchases. Purpose-built model for leaked secret detection (2026-10-07) · Oct 2026 · source · release history
example
-
Enable public monitoring for your data-residency enterprise to start receiving real-time alerts when credentials belonging to your verified domains are exposed in public commits.
In your GitHub Enterprise Cloud with data residency admin panel, go to Enterprise settings > Security and enable 'Public monitoring' under secret scanning.Public monitoring now available with data residency (2026-10-22) · Oct 2026 · source
Expiring CLI Credentials shipped Allows GitHub CLI users to request short-lived, automatically rotating OAuth tokens that expire within hours if leaked, with options to set this as the default for all future sign-ins, view token expiration status, and fall back gracefully on unsupported GHES versions.
Also counts toward: Command-line interface
release 8 total
- Existing sessions remain signed in after upgrading to 3.6.10, but existing tokens are not automatically migrated to short-lived tokens — new short-lived tokens are only issued at the next sign-in once the rollout reaches your installation. GitHub Desktop adds short-lived authentication tokens (2026-11-03) · Nov 2026 · source · release history
- Short-lived tokens are available on github.com and GitHub Enterprise Cloud via a gradual rollout; GitHub Enterprise Server is not included in this rollout. GitHub Desktop adds short-lived authentication tokens (2026-11-03) · Nov 2026 · source · release history
- Token renewal happens automatically for GitHub API requests and Git operations, so no manual re-authentication is needed during normal use.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub Desktop adds short-lived authentication tokens (2026-11-03) · Nov 2026 · source · release history
-
Extends
gh auth statusto show the expiration time of the current access token when expiring credentials are active. GitHub CLI: Opt in to expiring, auto-refreshing OAuth tokens (2026-10-21) · Oct 2026 · source · release history -
Adds
--expiringflag togh auth loginto request short-lived, automatically rotating OAuth tokens that become useless within hours if leaked.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub CLI: Opt in to expiring, auto-refreshing OAuth tokens (2026-10-21) · Oct 2026 · source · release history -
Scripts or extensions that run
gh auth token, store the result, and reuse it later will eventually hold an expired token — read it fresh each time withgh auth tokeninstead of caching it. GitHub CLI: Opt in to expiring, auto-refreshing OAuth tokens (2026-10-21) · Oct 2026 · source · release history
docs
- Authenticating with GitHub CLI Learn the ways to authenticate GitHub CLI, from interactive sign-in to environment variables, expiring tokens, and GitHub Actions. seen Oct 2026 · source
example
-
Make expiring tokens the default for every future sign-in on this machine without passing
--expiringeach time.gh config set expiring_credentials enabledGitHub CLI: Opt in to expiring, auto-refreshing OAuth tokens (2026-10-21) · Oct 2026 · source -
Configure gh as the git credential helper so expiring tokens are served and refreshed automatically for HTTPS git operations.
gh auth setup-gitGitHub CLI: Opt in to expiring, auto-refreshing OAuth tokens (2026-10-21) · Oct 2026 · source -
Opt in to expiring tokens for a single login so a leaked access token expires within hours rather than lasting indefinitely.
gh auth login --expiringGitHub CLI: Opt in to expiring, auto-refreshing OAuth tokens (2026-10-21) · Oct 2026 · source
Local Model Provider Configuration shipped Allows users to configure local model providers in the GitHub Copilot app so that locally hosted models appear in the model picker alongside cloud models, with support for offline mode via an environment variable.
Also counts toward: Command-line interface, Offline mode
release 7 total
-
Enable experimental mode and open
/modelin Copilot CLI to follow the managed setup prompts for local model download and configuration on Windows.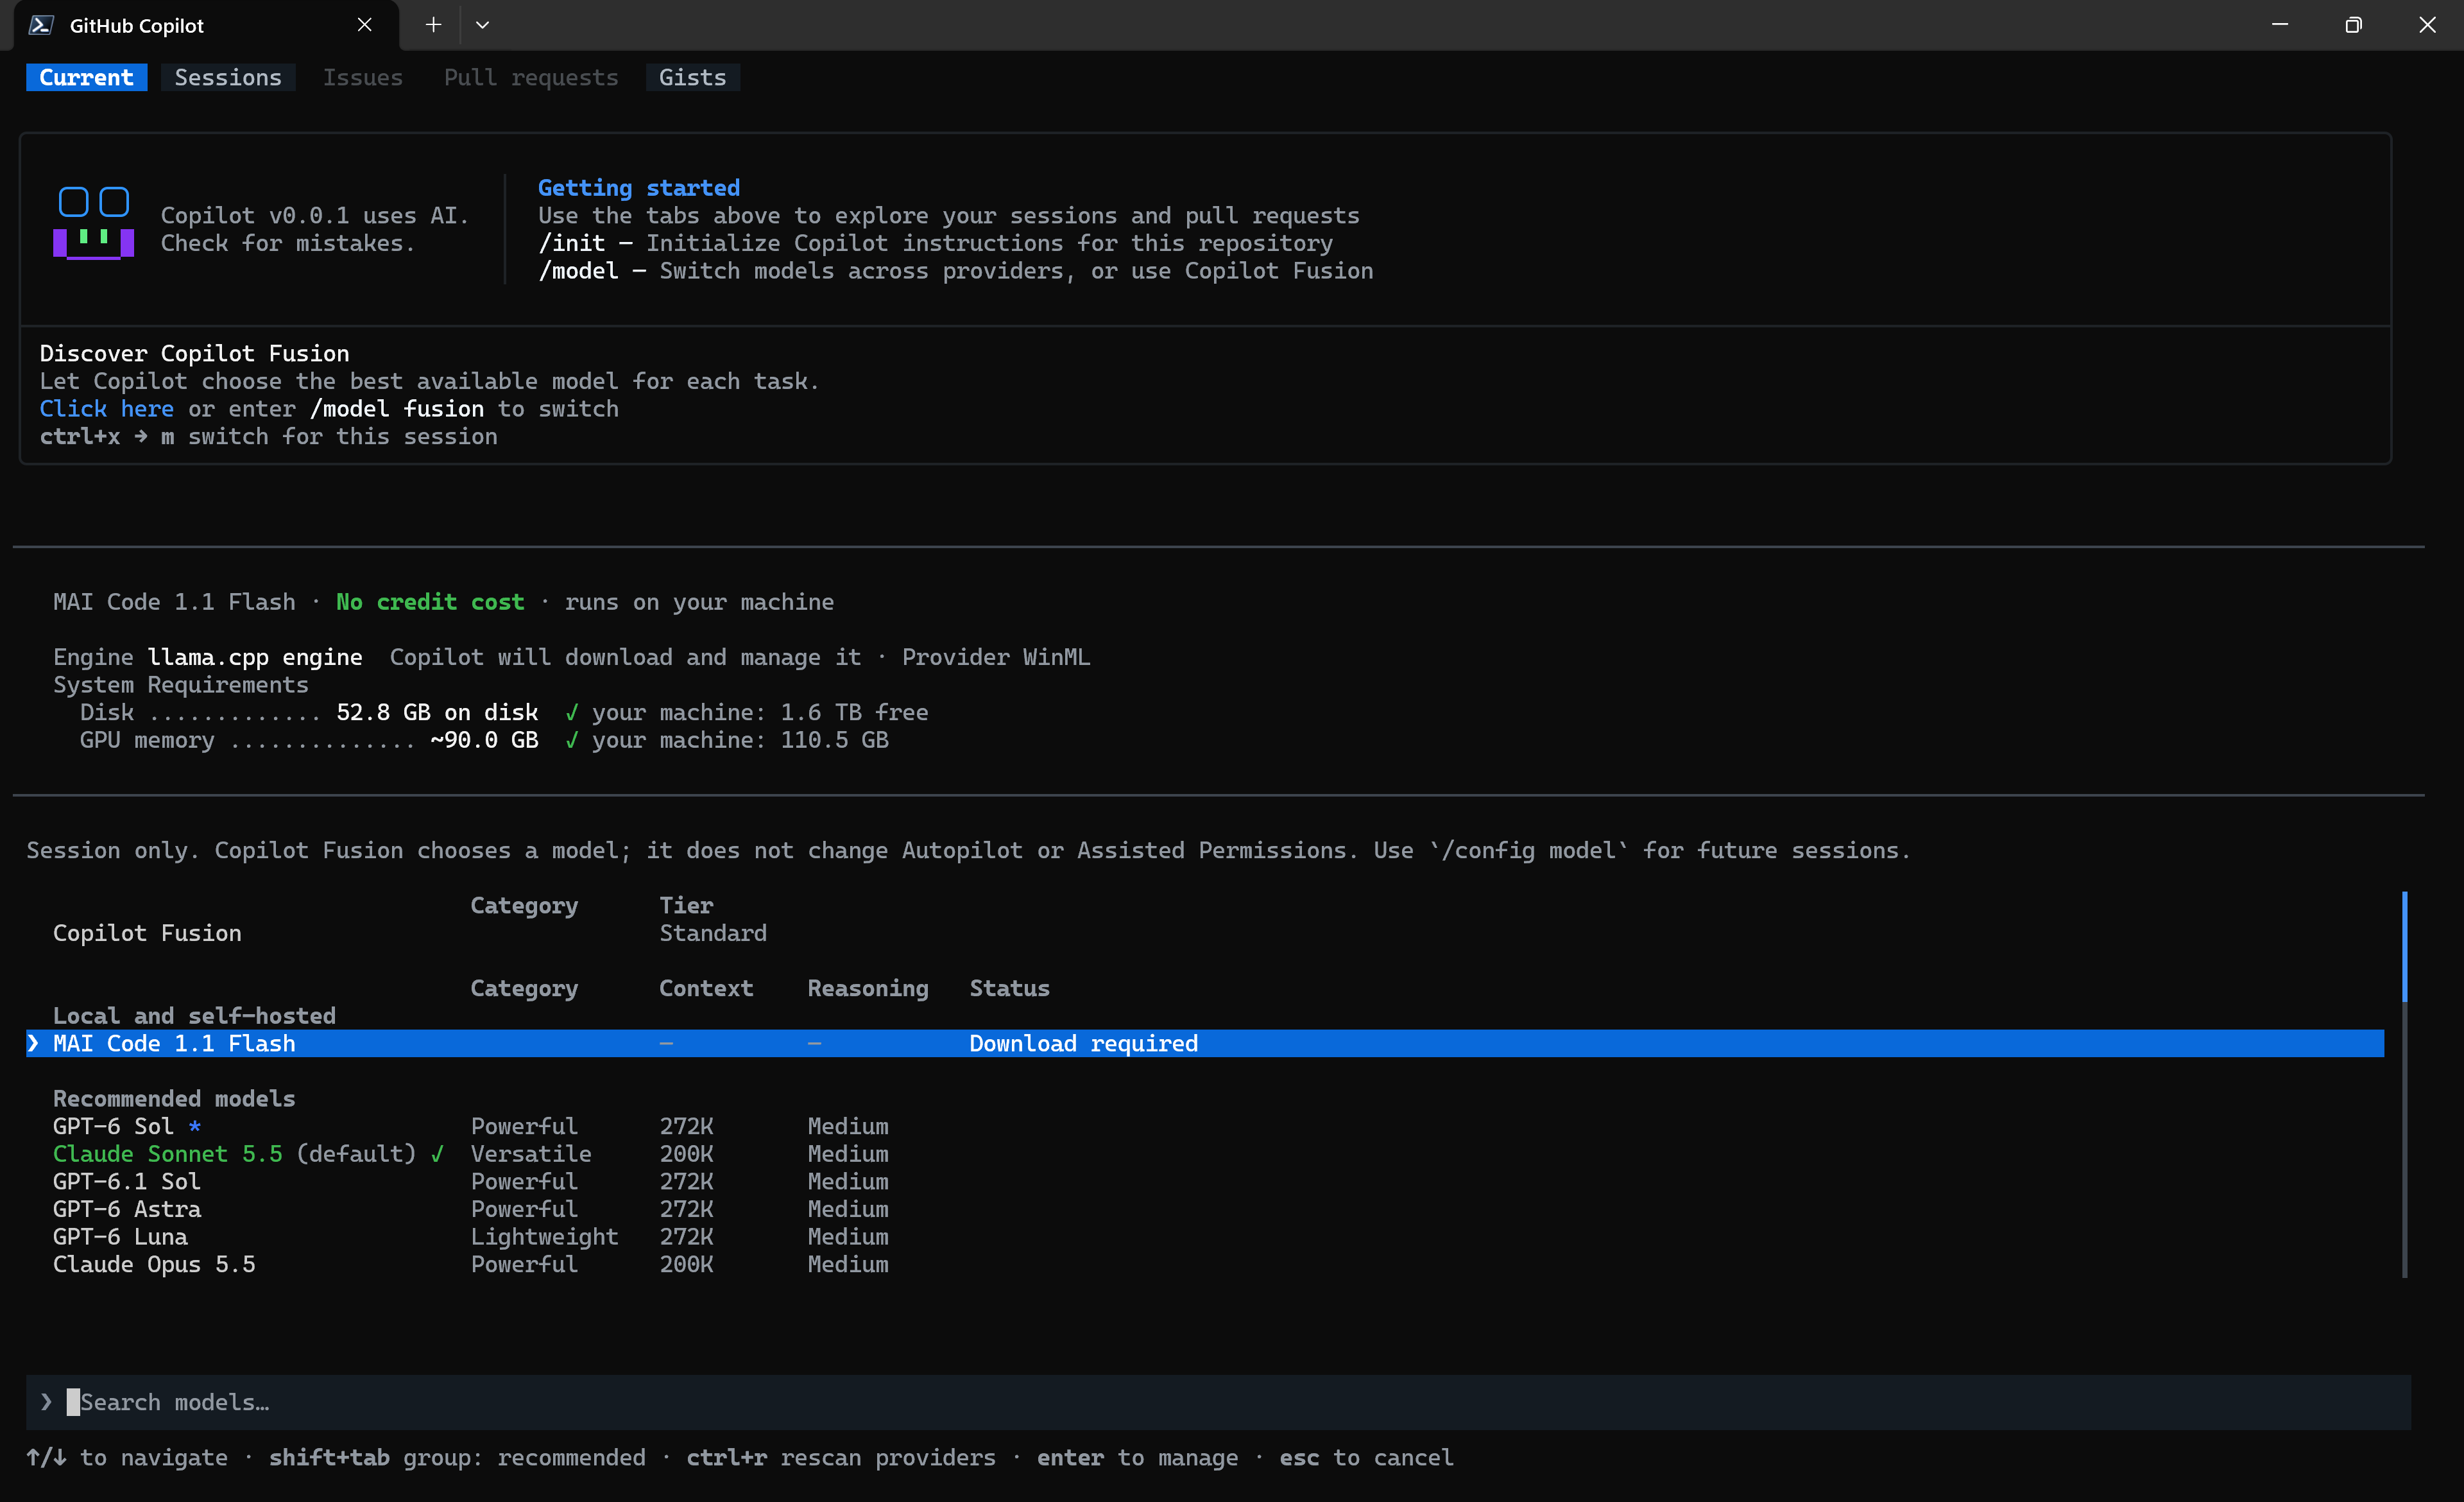 GitHub Copilot Fusion now supports selection of local models (2026-10-28) · Oct 2026
· source
· release history
-
Download and configure
MAI Code 1.1 Flashthrough the Windows ML provider on supported Windows devices via Settings > Model providers, then enable Local model auto routing under Settings > Experiments in the Copilot app. GitHub Copilot Fusion now supports selection of local models (2026-10-28) · Oct 2026 · source · release history -
Configure
MAI Code 1.1 FlashorQwen3.8 Flash Nextthrough a local OpenAI-compatible server on Windows, macOS, or Linux for bring-your-own local model routing in Copilot CLI. GitHub Copilot Fusion now supports selection of local models (2026-10-28) · Oct 2026 · source · release history - Adds a new MCP setting to disable automatic server startup for Copilot and Claude, giving administrators control over when configured tools become active.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New controls and chat improvements in Copilot for JetBrains (2026-10-10) · Oct 2026 · source · release history
-
Adds
/modelcommand in GitHub Copilot CLI to discover and select supported models from a running local Ollama instance alongside configured and cloud models.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
GitHub Copilot weekly releases — October 5 (2026-10-09) · Oct 2026
· source
· release history
- Adds local model provider configuration in the GitHub Copilot app at Settings > Model providers. Discover local models in GitHub Copilot CLI (2026-10-07) · Oct 2026 · source · release history
example
-
Enable local model routing in VS Code so Copilot Fusion can automatically pick between your on-device model and cloud models without manual switching.
chat.copilot.localModel.enabled: trueGitHub Copilot Fusion now supports selection of local models (2026-10-28) · Oct 2026 · source -
Disable automatic MCP server startup so Copilot and Claude tools only become active when you explicitly enable them — useful in restricted or air-gapped environments.
In the JetBrains IDE, go to Settings > GitHub Copilot > MCP and disable 'Automatic server startup' for Copilot and Claude.New controls and chat improvements in Copilot for JetBrains (2026-10-10) · Oct 2026 · source -
Switch to a locally-running model mid-workflow without leaving the CLI — useful when you want lower-latency or offline inference via Ollama.
/modelGitHub Copilot weekly releases — October 5 (2026-10-09) · Oct 2026 · source
Enterprise Credential Inventory and Audit shipped Provides administrators with the ability to view, filter, export, and manage metadata for all enterprise credentials via API and UI.
Also counts toward: CSV data export, Web management console
release 9 total
-
Adds filtering and sorting on the enterprise security dashboard by repository, committer, secret type, attribution method (
membershiporverified domain), and state (openorclosed). Public monitoring adds triage, validity, API, and webhooks (2026-10-23) · Oct 2026 · source · release history - Adds always-on validity checks for supported secret types that continuously display whether a credential is Active, Inactive, or Unknown, enabling teams to prioritize response for live tokens. Public monitoring adds triage, validity, API, and webhooks (2026-10-23) · Oct 2026 · source · release history
- Confidential comments are clearly marked in the advisory timeline and views are recorded in the audit log. Confidential comments on repository security advisories (2026-10-02) · Oct 2026 · source · release history
- Surfaces credential metadata in the inventory including owners, scopes and permissions, creation and expiration dates, last-used dates, and target organizations or repositories. GitHub Enterprise adds credential inventory exports (2026-09-21) · Sep 2026 · source · release history
- Adds new paginated REST API endpoints to programmatically retrieve the complete enterprise credential inventory for reporting and automation. GitHub Enterprise adds credential inventory exports (2026-09-21) · Sep 2026 · source · release history
- Adds a new View enterprise credentials fine-grained permission that grants members access to the enterprise credential inventory alongside enterprise owners.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub Enterprise adds credential inventory exports (2026-09-21) · Sep 2026 · source · release history
example
-
Export a one-off CSV snapshot of all enterprise credentials for offline review or audit when you don't need automation.
In your enterprise, go to Settings -> Authentication Security -> Credentials and click 'Export CSV' next to the 'Overview' section.GitHub Enterprise adds credential inventory exports (2026-09-21) · Sep 2026 · source
Unified Agent Policy Enforcement shipped Allows administrators to define and enforce unified policies for the Copilot experience across multiple surfaces, including mandatory opt-out handling and default model effort levels.
release 8 total
- Eligible generally available Copilot features and capabilities left Unconfigured will be automatically set to Enabled, Disabled, or Let organizations decide according to the selected global default — this is a one-time irreversible change; subsequent changes to the default policy will not revert features… Global default for Copilot features generally available (2026-10-22) · Oct 2026 · source · release history
- Applies the global default policy to eligible settings on the Features & clients and MCP servers in Copilot configuration surfaces. Global default for Copilot features generally available (2026-10-22) · Oct 2026 · source · release history
- Introduces a global default policy for generally available Copilot features, reachable via AI Controls → Copilot → Default policy for new features, that sets unconfigured eligible settings to Enabled, Disabled, or Let organizations decide on Copilot Business and Enterprise plans.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Global default for Copilot features generally available (2026-10-22) · Oct 2026 · source · release history
-
Adds
forceRemoteSettingsRefreshsetting (supported in server-managed, MDM-managed, and file-based delivery) to require Copilot clients to fetch current server-managed settings at startup rather than using a cached policy, failing closed if current policy cannot be confirmed.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enterprise managed settings enforcement updates (2026-10-13) · Oct 2026 · source · release history -
Enforces a minimum required client version on the
sandboxmanaged settings key, forcing users pinned to older Copilot client versions to update before Copilot will run. Enterprise managed settings enforcement updates (2026-10-13) · Oct 2026 · source · release history - Explicit managed values take precedence over local settings, SDK configuration, and environment variables. Client telemetry user attribution and configurable capture (2026-10-12) · Oct 2026 · source · release history
example
-
Review and set the global default before the October 26 rollout completes, to ensure unconfigured Copilot features land in the state your organization requires.
In the enterprise or organization console, go to AI Controls → Copilot → Default policy for new features and choose Enabled, Disabled, or Let organizations decide before the rollout takes effect for…Global default for Copilot features generally available (2026-10-22) · Oct 2026 · source
Audit Logging for Credential Actions shipped Captures credential revocation and deauthorization actions in the audit log with email notifications to affected users.
Also counts toward: Administrative audit log
release 8 total
-
On November 12, 2026, the
businessfield insecret_scanning_alert.*andsecret_scanning_push_protection.bypassaudit log events will change from the enterprise display name to the enterprise slug. Updates to GitHub secret scanning (2026-10-20) · Oct 2026 · source · release history - License policy changes now emit audit log events for integration with external systems of record. Open source license compliance generally available (2026-10-16) · Oct 2026 · source · release history
-
Adds
repo.code_quality_findings_dismissedaudit log event, recording who dismissed one or more backlog Code Quality findings, when, the repository and rule, and the identifiers and count of affected findings.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Audit GitHub Code Quality finding dismissals and reopenings (2026-10-13) · Oct 2026 · source · release history -
Adds
repo.code_quality_findings_reopenedaudit log event with the same metadata for reopened backlog findings. Audit GitHub Code Quality finding dismissals and reopenings (2026-10-13) · Oct 2026 · source · release history - Enables retrieval of both new events via the audit log API on GitHub Enterprise Cloud. Audit GitHub Code Quality finding dismissals and reopenings (2026-10-13) · Oct 2026 · source · release history
- Adds support for configuring Copilot CLI to work with GHES in disconnected or air-gapped environments — set up a model provider once in GHES and end users authenticate with their GHES credentials (technical preview). GitHub Enterprise Server 3.22 is now generally available (2026-09-08) · Sep 2026 · source · release history
example
-
Filter your organization audit log to see all Code Quality finding dismissals across repositories — useful for compliance reviews or investigating when sensitive findings were suppressed.
In the organization audit log, filter by action name `repo.code_quality_findings_dismissed` to list all dismissal events with actor, timestamp, repository, rule, and affected finding IDs.Audit GitHub Code Quality finding dismissals and reopenings (2026-10-13) · Oct 2026 · source
Session History and Navigation shipped Provides mechanisms to search, navigate, and restore agent sessions across the unified interface.
Also counts toward: Command-line interface
release 8 total
-
Adds
repo.code_quality_findings_reopenedaudit log event with the same metadata for reopened backlog findings. Audit GitHub Code Quality finding dismissals and reopenings (2026-10-13) · Oct 2026 · source · release history - Chat messages are now grouped by turn with controls for moving quickly between turns. New controls and chat improvements in Copilot for JetBrains (2026-10-10) · Oct 2026 · source · release history
- Adds hierarchical sessions list view so agents can create new chats or sessions and users can navigate back to the source chat via a navigation link. GitHub Copilot in VS Code, September 2026 releases (2026-10-01) · Oct 2026 · source · release history
- Adds Mark as Done suggestions and automatic cleanup to keep completed sessions organized (preview). GitHub Copilot in VS Code, September 2026 releases (2026-10-01) · Oct 2026 · source · release history
- Adds application badge support (preview) to surface new results, input requests, and PR checks on the dock, launcher, or taskbar. GitHub Copilot in VS Code, September 2026 releases (2026-10-01) · Oct 2026 · source · release history
- Adds ability to view and continue recent Copilot or Claude agent sessions created in other applications from the Sessions list in VS Code. GitHub Copilot in VS Code, August 2026 releases (2026-08-31) · Aug 2026 · source · release history
example
-
Filter your organization audit log to see all Code Quality finding dismissals across repositories — useful for compliance reviews or investigating when sensitive findings were suppressed.
In the organization audit log, filter by action name `repo.code_quality_findings_dismissed` to list all dismissal events with actor, timestamp, repository, rule, and affected finding IDs.Audit GitHub Code Quality finding dismissals and reopenings (2026-10-13) · Oct 2026 · source
Security Advisory GraphQL Enhancements shipped Extends the SecurityAdvisory GraphQL object with additional fields and filters, including NVD publish date, GitHub review date, source code location, repository advisory URL, and severity or withdrawal filters.
Also counts toward: GraphQL API support
release 7 total
-
Adds
cveId,sourceCodeLocation,githubReviewedAt,nvdPublishedAt, andrepositoryAdvisoryUrlfields to theSecurityAdvisoryGraphQL object New fields for SecurityAdvisory GraphQL API (2026-10-02) · Oct 2026 · source · release history -
Adds
sourceCodeLocationfield to theSecurityAdvisoryGraphQL object linking to affected source code relevant to the advisory. New fields for SecurityAdvisory GraphQL API (2026-10-02) · Oct 2026 · source · release history -
Adds
severitiesandisWithdrawnfilters to thesecurityAdvisoriesGraphQL query, enabling server-side narrowing of advisory results without downloading and filtering client-side.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ New fields for SecurityAdvisory GraphQL API (2026-10-02) · Oct 2026 · source · release history -
Adds
nvdPublishedAtfield to theSecurityAdvisoryGraphQL object exposing when the NVD published its record. New fields for SecurityAdvisory GraphQL API (2026-10-02) · Oct 2026 · source · release history -
Adds
githubReviewedAtfield to theSecurityAdvisoryGraphQL object exposing when GitHub reviewed the advisory. New fields for SecurityAdvisory GraphQL API (2026-10-02) · Oct 2026 · source · release history -
Adds
repositoryAdvisoryUrlfield to theSecurityAdvisoryGraphQL object linking to the associated repository security advisory when one exists. New fields for SecurityAdvisory GraphQL API (2026-10-02) · Oct 2026 · source · release history
example
-
Retrieve key advisory metadata including CVE ID and review timestamps in a single query
{ securityAdvisories(severities: HIGH, isWithdrawn: false) { edges { node { cveId sourceCodeLocation githubReviewedAt nvdPublishedAt } } } }New fields for SecurityAdvisory GraphQL API (2026-10-02) · Oct 2026 · source -
Filter advisories by severity and withdrawal status to build a triage feed
{ securityAdvisories(severities: [CRITICAL, HIGH]) { totalCount } }New fields for SecurityAdvisory GraphQL API (2026-10-02) · Oct 2026 · source
Agent Task Scheduling shipped Enables scheduling recurring agent tasks or triggering them on demand via agentic automations.
Also counts toward: Scheduled jobs
release
- Shared automations belong to the repository and persist if the creator leaves the team, with a change history showing how tools, triggers, and prompts have evolved. Build shared workflows for your team with Copilot Automations (2026-10-28) · Oct 2026 · source · release history
- Shared Copilot Automations are available on Copilot Pro, Pro+, Max, Business, and Enterprise plans. Build shared workflows for your team with Copilot Automations (2026-10-28) · Oct 2026 · source · release history
-
GitHub Copilot Projects now support automations for repeatable tasks, such as triggering a workflow whenever a specific event occurs.
GitHub Copilot app, Universe releases (2026-10-28) · Oct 2026
· source
· release history
- Create shared Copilot Automations by choosing Shared under Type when creating an automation on github.com, the GitHub Copilot app, or Visual Studio Code — making the workflow visible to all readers and editable by anyone with write access.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Build shared workflows for your team with Copilot Automations (2026-10-28) · Oct 2026 · source · release history
- Adds automations to schedule recurring agent tasks on an hourly, daily, or weekly cadence, or run them on demand from a template or custom prompt (preview). GitHub Copilot in VS Code, September 2026 releases (2026-10-01) · Oct 2026 · source · release history
-
Adds agent automations (public preview) in VS Code 1.137, enabling recurring agent tasks scheduled hourly, daily, or weekly, or triggered on demand.
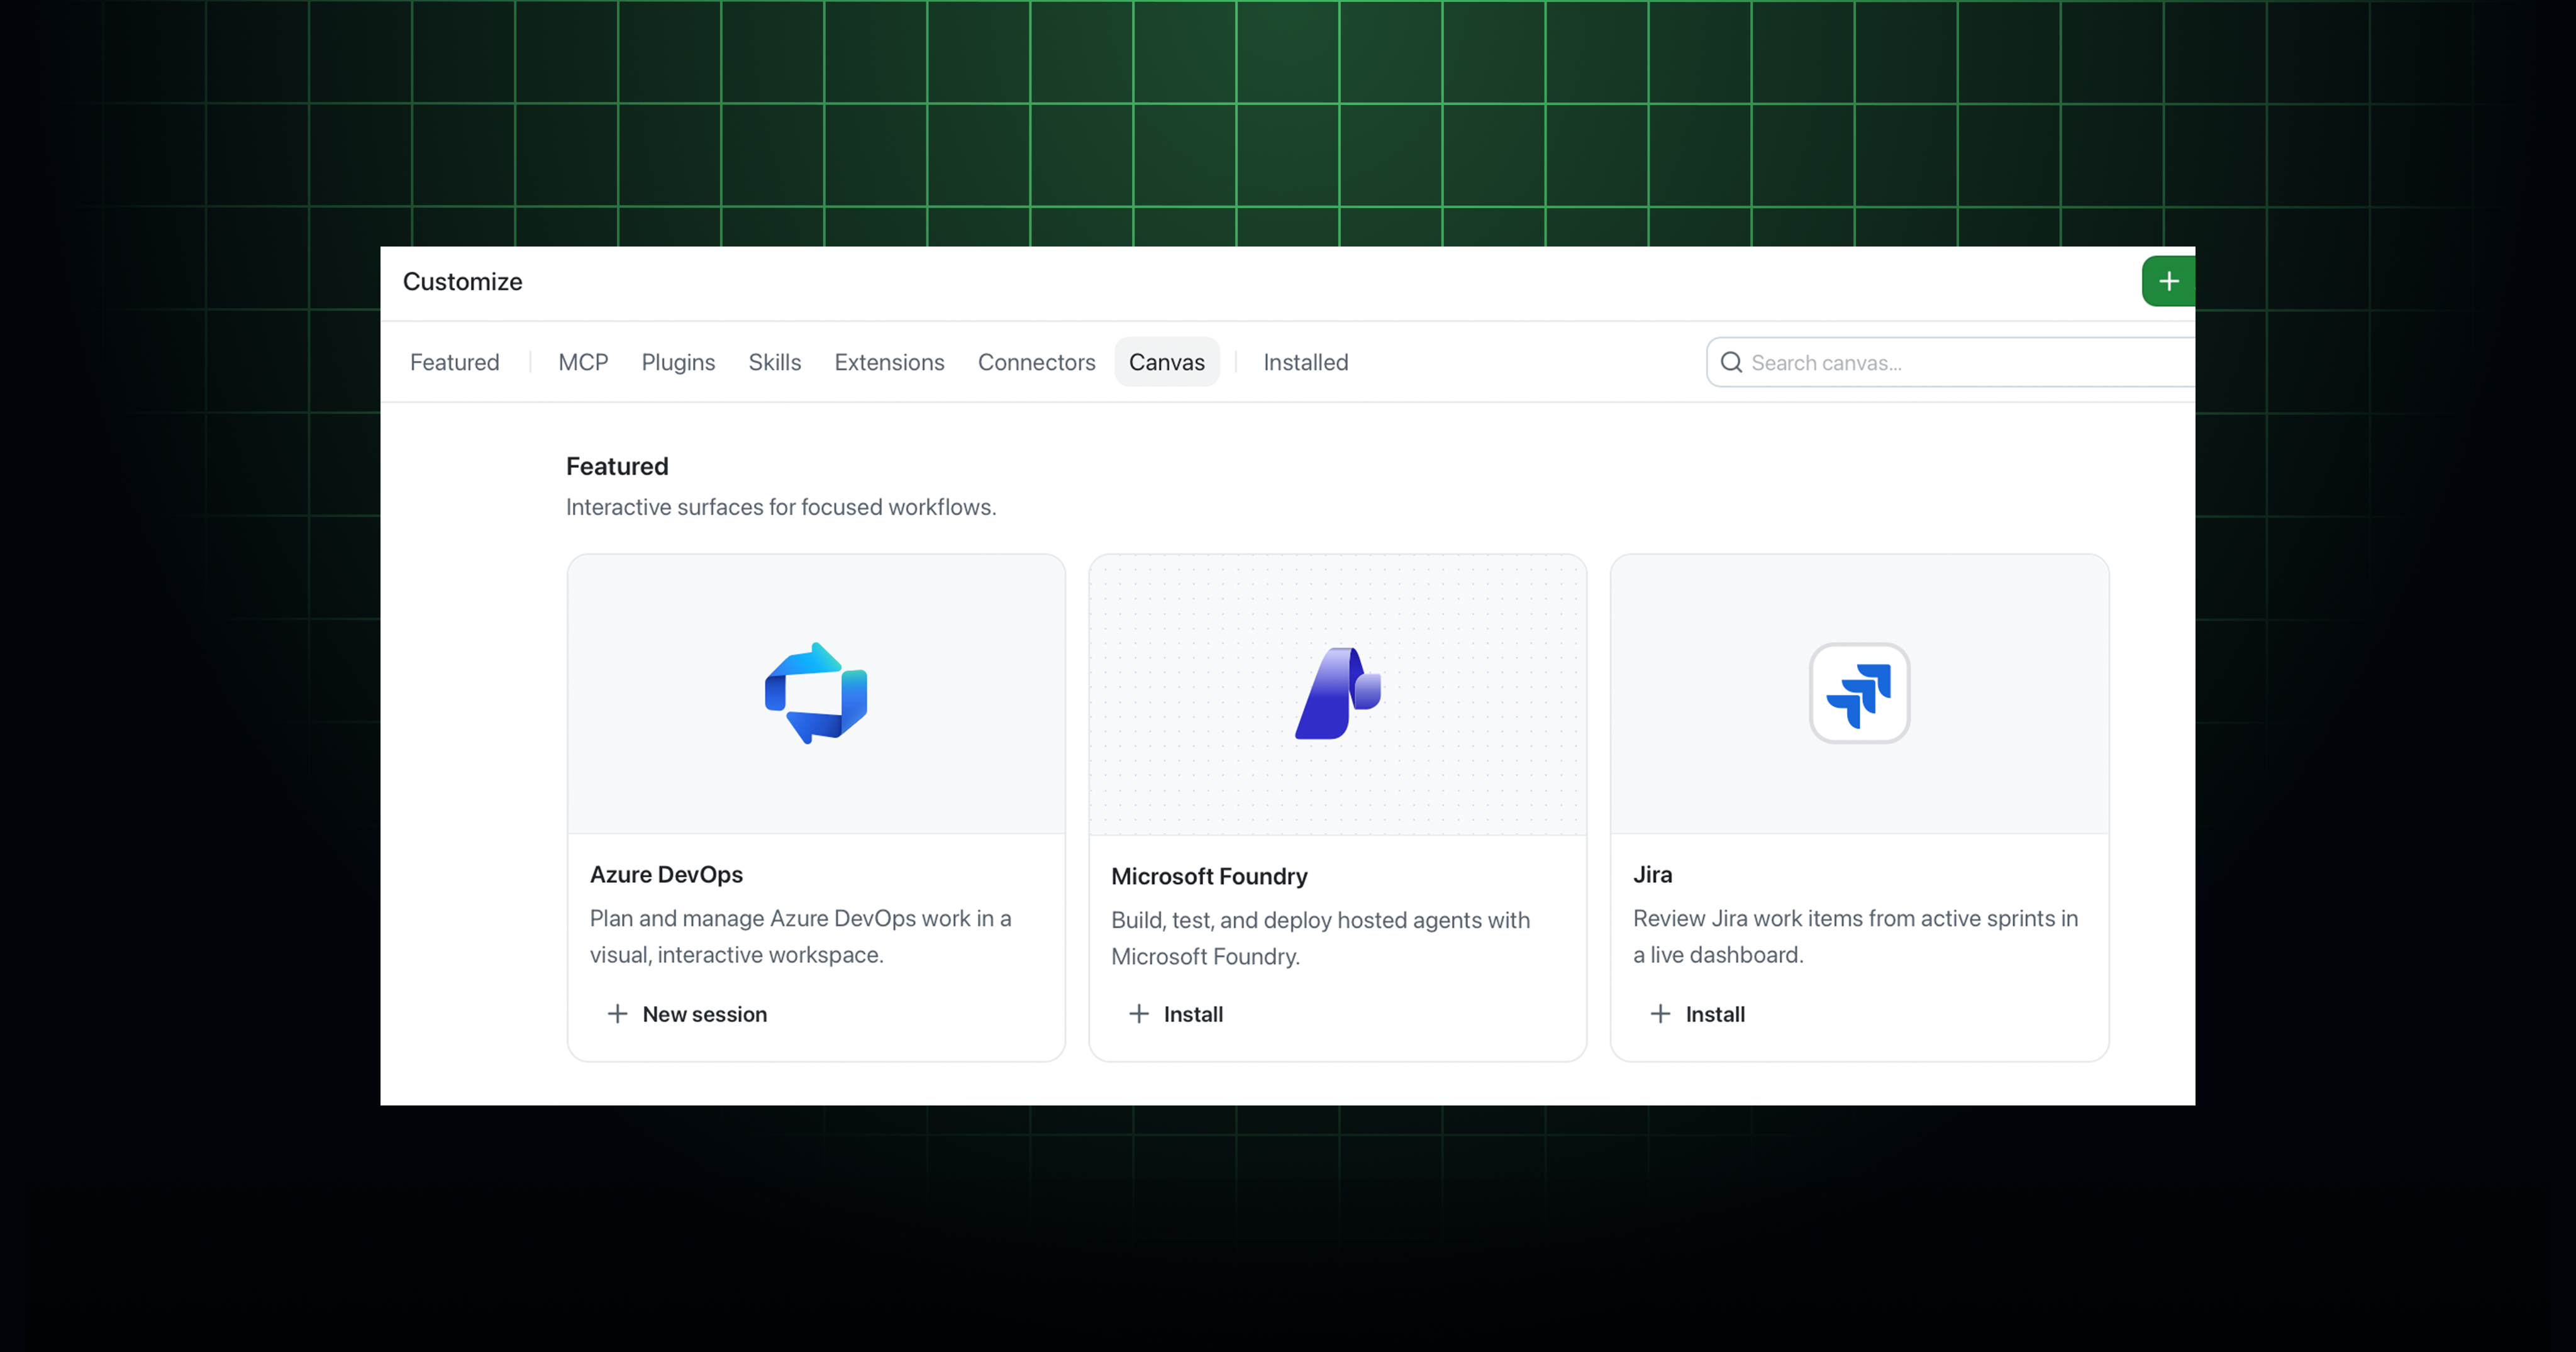 GitHub Copilot weekly releases — September 7 (2026-09-10) · Sep 2026
· source
· release history
example
-
Create a team-owned automation — for example, to automatically investigate production incidents — so it survives individual team members leaving.
On github.com, open a repository where you have write access, navigate to Copilot Automations > New automation, set triggers and tools, then under Type select 'Shared' before saving.Build shared workflows for your team with Copilot Automations (2026-10-28) · Oct 2026 · source -
Run a nightly dependency-audit prompt against your repo without manual intervention.
In the Agents window, select 'New Automation', choose a daily schedule, and enter your prompt (or pick a template) to have Copilot run the task automatically each day.GitHub Copilot in VS Code, September 2026 releases (2026-10-01) · Oct 2026 · source
Session Continuity shipped Ensures agent sessions can be started, continued, or handed off seamlessly across different development environments and applications.
Also counts toward: Import from a competing product
release 7 total
-
Introduces the new Agent Host, which isolates Copilot sessions from individual VS Code windows: it powers session continuity across VS Code, the GitHub Copilot app, GitHub Mobile, github.com, Copilot CLI, Slack, and Microsoft Teams DMs; lets you control an agent running on your development machine from GitHub Mobile…
GitHub Copilot in VS Code, Universe releases (2026-10-28) · Oct 2026
· source
· release history
- Switch between the editor and the Agents window without losing context — both views stay in sync with the same live Copilot session. GitHub Copilot in VS Code, Universe releases (2026-10-28) · Oct 2026 · source · release history
- Enables smoother repository switching mid-conversation in Slack and Microsoft Teams. Multi-repo support and other improvements for GitHub Copilot in Slack and Microsoft Teams (2026-10-16) · Oct 2026 · source · release history
- Improves repository switching so users can move between repositories more easily mid-conversation. Multi-repository support and other improvements for GitHub in Slack and Teams (2026-10-16) · Oct 2026 · source · release history
- Enables picking up a Codex conversation from the ChatGPT app inside VS Code to continue work on a codebase without copying context or files. GitHub Copilot in VS Code, September 2026 releases (2026-10-01) · Oct 2026 · source · release history
-
Adds automatic inactive-session cleanup in VS Code (opt-in, now in preview): marks sessions as Done once all their pull requests merge, with optional deletion after a configurable grace period.
GitHub Copilot weekly releases — September 14 (2026-09-18) · Sep 2026
· source
· release history
example
-
Start a remote agent host so you can control a long-running coding task from your phone or another device while your development machine keeps working.
code agent host --github-environmentGitHub Copilot in VS Code, Universe releases (2026-10-28) · Oct 2026 · source
Agent Code Fix Automation shipped Enables the agent to autonomously fix code quality findings by analyzing them, generating validated fixes on a branch, and opening a pull request for review.
Also counts toward: Autonomous investigation and remediation, Built-in AI assistant
release
- Adds a fixer action on NuGet Audit warnings in the Error List that opens Copilot Chat in agent mode and uses the NuGet MCP server to fix vulnerable packages — requires signing in to GitHub Copilot and enabling the NuGet MCP server from the Copilot Chat tools menu. GitHub Copilot in Visual Studio — September update (2026-10-23) · Oct 2026 · source · release history
- Adds agent merge in active sessions (preview) to let the agent handle review feedback, failed checks, merge conflicts, and workflow reruns. GitHub Copilot in VS Code, September 2026 releases (2026-10-01) · Oct 2026 · source · release history
- Adds Assign to Copilot bulk action that lets you select up to 25 standard Code Quality findings and have Copilot fix them agentically on a branch, validate its own changes, and open a pull request for review.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Remediate Code Quality findings with agentic autofix (2026-09-09) · Sep 2026 · source · release history
example
-
Trigger an AI-assisted fix for a vulnerable NuGet package the moment Visual Studio flags it in the Error List.
1. In the Error List, locate a NuGet Audit warning for a vulnerable package. 2. Click the fixer action on the warning. 3.GitHub Copilot in Visual Studio — September update (2026-10-23) · Oct 2026 · source -
Assign a specific code scanning alert to Copilot for autonomous remediation via the REST API, triggering file exploration, fix generation, CodeQL validation, and a draft PR.
curl -X PATCH \ -H 'Authorization: Bearer <token>' \ -H 'Accept: application/vnd.github+json' \ https://api.github.com/repos/<owner>/<repo>/code-scanning/alerts/<alert_number> \ -d '{"assignees":…Agentic autofix for code scanning alerts general availability (2026-10-15) · Oct 2026 · source -
Enable agentic autofix for an organization after the enterprise administrator has turned on the Agentic autofix policy, so Copilot can begin remediating code scanning alerts.
In GitHub Enterprise Cloud, go to Enterprise Settings > Advanced Security policies > Agentic autofix and enable the policy.Agentic autofix for code scanning alerts general availability (2026-10-15) · Oct 2026 · source -
Hand off post-PR-creation chores to the agent so you can focus on the next task instead of babysitting CI.
In the Agents window, open an active agent session, then select 'Enable agent merge' to let the agent automatically respond to review feedback, resolve merge conflicts, rerun failed checks, and merge…GitHub Copilot in VS Code, September 2026 releases (2026-10-01) · Oct 2026 · source -
Burn down a backlog of code quality findings by assigning a batch to Copilot, which opens a PR with validated fixes for each one.
In your repository, go to Code Quality > Findings. Select up to 25 standard findings using the checkboxes, then choose 'Assign to Copilot' from the bulk-action menu.Remediate Code Quality findings with agentic autofix (2026-09-09) · Sep 2026 · source
npm Trusted Publishing Configuration Lifecycle shipped Manages the lifecycle of npm trusted publishing configurations, including 48-hour expiration windows for unvalidated configurations, visibility of expired configurations without counting toward limits, and reset of trust on identity changes.
release 7 total
- You cannot change the authentication method of an existing registry — to switch a placeholder-token registry to Anonymous, you must delete it and re-create it via Settings > Secrets and variables > Private registries > New private registry. Anonymous organization-level registries for Dependabot (2026-10-12) · Oct 2026 · source · release history
- Adds Anonymous as a selectable authentication method for organization-level private registries in Dependabot, enabling registries that allow unauthenticated reads (such as internal package mirrors) without requiring a placeholder token workaround.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Anonymous organization-level registries for Dependabot (2026-10-12) · Oct 2026 · source · release history
-
Organization-level private registries configured with Anonymous authentication apply to every granted repository, including those using only Dependabot security updates with no
dependabot.ymlfile. Anonymous organization-level registries for Dependabot (2026-10-12) · Oct 2026 · source · release history - Expired configurations remain visible in trusted publisher settings but do not count toward per-package limits. Unvalidated npm trusted publishing configurations now expire (2026-10-02) · Oct 2026 · source · release history
- Unvalidated npm trusted publishing configurations expire 48 hours after creation and can no longer authorize publishing until a successful publish validates them.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Unvalidated npm trusted publishing configurations now expire (2026-10-02) · Oct 2026 · source · release history
- Unvalidated trusted publishing configurations older than 48 hours can no longer authorize publishing; affected configurations must be recreated to start a new 48-hour window. Unvalidated npm trusted publishing configurations now expire (2026-10-02) · Oct 2026 · source · release history
example
-
Add a credential-free internal package mirror as an organization-level Dependabot registry so all granted repos can reach it without a token.
In your organization, go to Settings > Secrets and variables > Private registries > New private registry, enter the registry URL, and set the authentication method to `Anonymous`.Anonymous organization-level registries for Dependabot (2026-10-12) · Oct 2026 · source
Pull Request List and Management Enhancements shipped Improves visibility and bulk operations for pull requests, including advanced search filters, status indicators, and batch actions.
release
- Compact presentation mode fits more pull requests on the page. Refreshed repository pull requests page generally available (2026-09-22) · Sep 2026 · source · release history
- Pull request list now surfaces status check counts, stack indicators, and unread-update indicators. Refreshed repository pull requests page generally available (2026-09-22) · Sep 2026 · source · release history
- Bulk actions let you close, label, or change milestones on one or more pull requests at once. Refreshed repository pull requests page generally available (2026-09-22) · Sep 2026 · source · release history
-
Advanced search on the pull requests page now supports
ANDandORkeywords as well as nested searches.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Refreshed repository pull requests page generally available (2026-09-22) · Sep 2026 · source · release history - Clicking a review status in the list filters pull requests by that status. Refreshed repository pull requests page generally available (2026-09-22) · Sep 2026 · source · release history
example
-
Triagers handling spam or abandoned PRs can now archive them directly in the UI without escalating to an admin.
In the pull request page, open the pull request actions menu and select 'Archive pull request'. The PR will be closed and its conversation made read-only immediately.Triage role users or higher can now archive pull requests (2026-10-08) · Oct 2026 · source -
Narrow a busy repository's PR list to open, approved PRs that still need a specific team's attention — combining OR and AND in one query.
In the repository pull requests page, enter into the search bar: is:open review:approved AND (involves:@my-org/security-team OR involves:@my-org/platform-team)Refreshed repository pull requests page generally available (2026-09-22) · Sep 2026 · source -
Quickly close or re-label a batch of stale PRs without opening each one individually.
In the repository pull requests page, check the checkboxes next to the target pull requests, then open the 'Label' or 'Close' bulk-action menu that appears at the top of the list.Refreshed repository pull requests page generally available (2026-09-22) · Sep 2026 · source
Collaborative Agent Workflows shipped Allows multiple team members to join, guide, and view agent sessions initiated from chat platforms, making the process transparent and interactive.
release 7 total
-
Ask Copilot about alerts in chat using the security extension's tools, governed by your existing tool permission settings.
Security extension for the GitHub Copilot app (2026-10-28) · Oct 2026
· source
· release history
- Supports querying across multiple repositories in a single Copilot conversation in Slack and Microsoft Teams, enabling PR tracking, issue investigation, and activity summaries without switching conversations.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Multi-repo support and other improvements for GitHub Copilot in Slack and Microsoft Teams (2026-10-16) · Oct 2026 · source · release history
- Agent Merge is now in public preview in VS Code 1.136, resolving review feedback, failed checks, and merge conflicts to get pull requests merge-ready. GitHub Copilot weekly releases — August 31 (2026-09-04) · Sep 2026 · source · release history
-
Adds
@GitHubmention support in Microsoft Teams channels, threads, and direct messages to start a GitHub Copilot cloud agent session that all conversation participants can view and direct. Shared agentic work with GitHub Copilot in Microsoft Teams (2026-08-21) · Aug 2026 · source · release history - Agent sessions are multiplayer — any team member can join from the original thread, add context, redirect the approach, or stop the session, making agent workflows visible and learnable across the team. The new GitHub Copilot experience in Slack (2026-08-21) · Aug 2026 · source · release history
-
Supports
@GitHub helpto list available commands from within Teams. Shared agentic work with GitHub Copilot in Microsoft Teams (2026-08-21) · Aug 2026 · source · release history
Secret Scanning Alert Resolution Enforcement shipped suggested Allows administrators to enforce rules that block pull request merges until all secret scanning alerts introduced in the changes are resolved, supporting both UI configuration and API endpoints.
Suggested capability: Static application security testing. This is our guess, not confirmed.
Also counts toward: REST API, Web management console
release
- Expands base64-encoded token revocation (public preview) in private and internal repositories on github.com to support encoded personal access tokens (classic), fine-grained personal access tokens, OAuth access tokens, and GitHub App user access tokens — GitHub automatically decodes the value. Updates to GitHub secret scanning (2026-10-20) · Oct 2026 · source · release history
- Adds new API endpoints for downloading, updating, and replacing the enterprise license policy, plus a separate endpoint for checking whether individual packages comply with policy.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Open source license compliance generally available (2026-10-16) · Oct 2026 · source · release history
- Introduces a Require license compliance results before merging ruleset condition that enforces an enterprise-wide license policy on pull requests adding or modifying dependencies. Open source license compliance generally available (2026-10-16) · Oct 2026 · source · release history
- Adds Require secret scanning alerts are resolved ruleset rule in repository, organization, and enterprise settings under Repository > Rulesets, blocking PR merges until all introduced secret alerts are cleared. Block pull requests with exposed secrets from merging (2026-09-09) · Sep 2026 · source · release history
-
Adds
require_secret_scanning_alert_resolutionrule type to the REST API (with asecret_typesparameter) to block PRs from merging when open secret scanning alerts exist.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Block pull requests with exposed secrets from merging (2026-09-09) · Sep 2026 · source · release history -
Supports configuring the rule to block additional secret categories beyond default provider patterns, such as custom or generic patterns, via the
secret_typesparameter. Block pull requests with exposed secrets from merging (2026-09-09) · Sep 2026 · source · release history
example
-
Enable the secret scanning alert resolution rule via the UI to protect your default branch without writing any API calls.
1. Go to your repository (or organization/enterprise) Settings. 2. Navigate to Repository > Rulesets. 3. Create or edit a ruleset targeting your protected branches. 4.Block pull requests with exposed secrets from merging (2026-09-09) · Sep 2026 · source
AI Scan for Pull Requests Coverage Visibility shipped suggested Surfaces AI Scan for pull requests enablement status in the security overview coverage view, with per-repository rows, summary counts, filter qualifiers, and CSV export support.
Suggested capability: Static application security testing. This is our guess, not confirmed.
Also counts toward: CSV data export
release
- AI Scan runs automatically on pull requests when code scanning and the repository's effective AI Scan setting are enabled — no GitHub Copilot license required. AI Scan for pull requests generally available (2026-10-15) · Oct 2026 · source · release history
- Adds an AI Scan tab to the Code scanning on pull requests page in security overview, showing total findings, autofix suggestion coverage, remediation rate, and developer adoption of autofix across repositories.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Code scanning AI Scan metrics in security overview (2026-10-13) · Oct 2026 · source · release history
- Renames the CodeQL pull requests page to Code scanning on pull requests and splits existing CodeQL metrics into a separate CodeQL tab alongside the new AI Scan tab. Code scanning AI Scan metrics in security overview (2026-10-13) · Oct 2026 · source · release history
-
Adds
code-scanning-ai-scan-pr-scan:enabledandcode-scanning-ai-scan-pr-scan:not-enabledfilter qualifiers to the security overview coverage view to isolate repositories by AI Scan for pull requests status.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄
Code scanning AI Scan enablement status in security overview (2026-10-06) · Oct 2026
· source
· release history
-
Adds a Code Scanning AI Scan for pull requests column (values:
enabled,not-enabled) to the coverage CSV export. Code scanning AI Scan enablement status in security overview (2026-10-06) · Oct 2026 · source · release history - Shows AI Scan for pull requests enablement status in the security overview coverage view, including per-repository rows and summary counts of enabled and not-enabled repositories. Code scanning AI Scan enablement status in security overview (2026-10-06) · Oct 2026 · source · release history
example
-
Review AI Scan effectiveness across your organization before deciding on a broader rollout.
In Security Overview, go to 'Code scanning on pull requests' > 'AI Scan' tab, then filter by reporting period to see total findings, remediation rate, and how often developers applied autofix…Code scanning AI Scan metrics in security overview (2026-10-13) · Oct 2026 · source
Staged npm Package Publishing shipped Allows npm packages to be created and published via a staged workflow where new versions enter a queue and require maintainer promotion before becoming installable, supporting creation of brand-new packages from CI without a manual first publish.
Also counts toward: Command-line interface
release
-
Adds a
withdrawnaction to thedependabot_alertwebhook event, with a payload containing the alert number, GHSA and CVE IDs, package, and manifest path captured before removal.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Improved detection for withdrawn Dependabot alerts (2026-10-13) · Oct 2026 · source · release history -
REST API requests to get or update a withdrawn Dependabot alert now return
410 Goneinstead of404 Not Found, allowing callers to distinguish withdrawn alerts from alerts that never existed. Improved detection for withdrawn Dependabot alerts (2026-10-13) · Oct 2026 · source · release history - After package creation via staged publish, package settings and trusted publishing can be configured immediately. npm staged publishing now supports creating new packages (2026-10-02) · Oct 2026 · source · release history
- First-version publishes via staged workflow enter a queue and require a maintainer to promote before the version becomes installable. npm staged publishing now supports creating new packages (2026-10-02) · Oct 2026 · source · release history
-
Enables
npm stage publishto create new npm packages (public scoped, unscoped, and private scoped) without a manual first publish, using a local session or a granular access token including a stage-only token.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ npm staged publishing now supports creating new packages (2026-10-02) · Oct 2026 · source · release history -
Enables
npm stage publishto create new scoped and unscoped packages from workflows npm staged publishing now supports creating new packages (2026-10-02) · Oct 2026 · source · release history
example
-
Bootstrap a brand-new npm package from CI without a manual first publish — the version enters the staged queue awaiting maintainer promotion.
npm stage publishnpm staged publishing now supports creating new packages (2026-10-02) · Oct 2026 · source
Assisted Permissions Mode shipped Adds an 'Assisted' permission mode across Copilot CLI, VS Code, and the Copilot app that lets an LLM automatically approve clearly safe commands, file-system access, and URL opens, with enterprise controls to set the default mode, block 'Allow All', or disable 'Assisted' entirely.
Also counts toward: Command-line interface
release
-
Enables Assisted permission mode in GitHub Copilot CLI via
/permissionscommand — selectassistedto let an LLM auto-approve clearly safe commands, file-system access, and URL opens.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄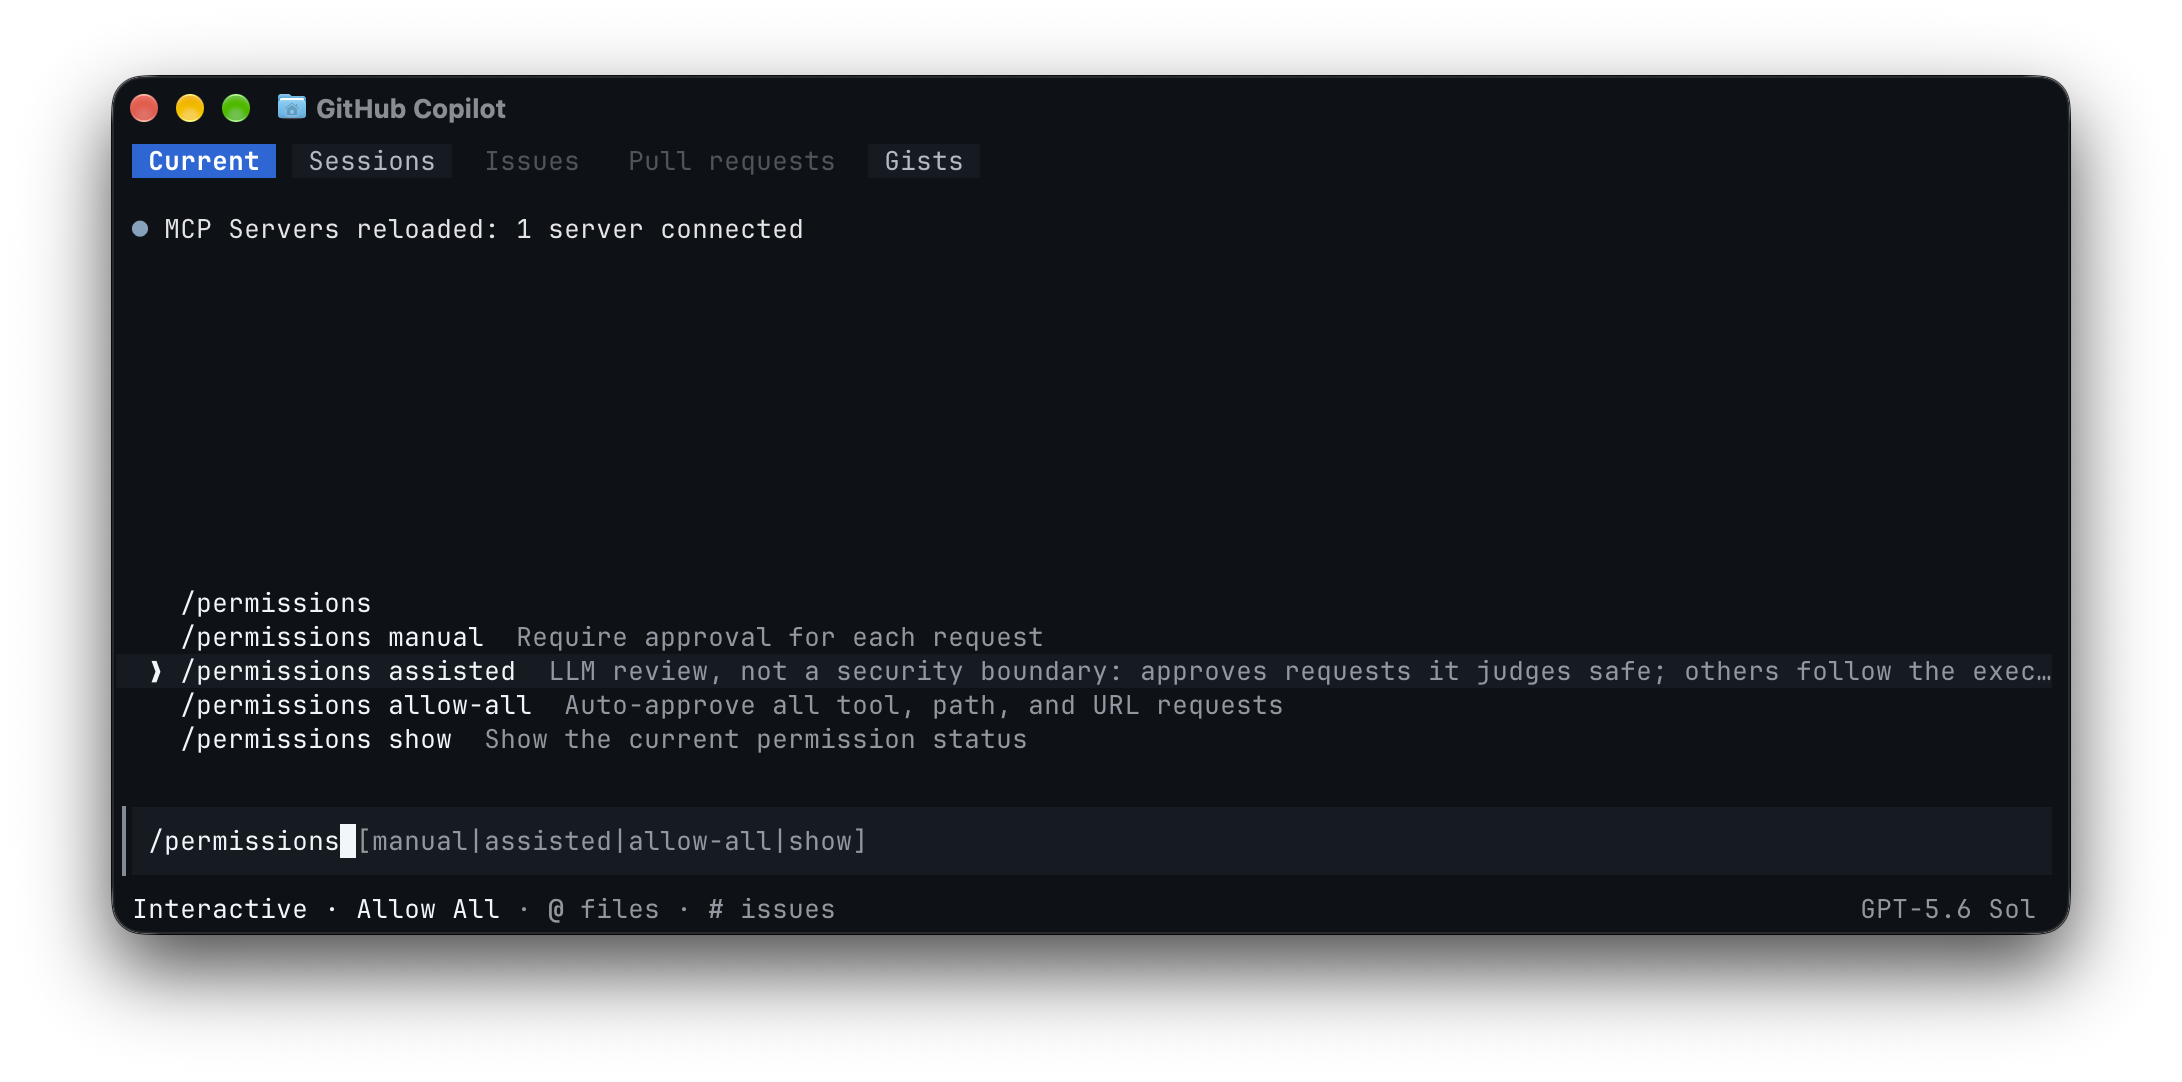 GitHub Copilot assisted permissions generally available (2026-10-26) · Oct 2026
· source
· release history
- Adds Assisted permissions mode in the GitHub Copilot app via Tool permissions in the mode picker. GitHub Copilot assisted permissions generally available (2026-10-26) · Oct 2026 · source · release history
- Provides enterprise-managed settings to block Allow All while keeping Assisted available, disable Assisted separately, and set the default permission mode for new sessions. GitHub Copilot assisted permissions generally available (2026-10-26) · Oct 2026 · source · release history
- Adds Assisted permissions mode in Visual Studio Code via the permissions picker. GitHub Copilot assisted permissions generally available (2026-10-26) · Oct 2026 · source · release history
example
-
Switch to assisted permissions in the Copilot CLI so safe commands run without interrupting your workflow.
/permissions # Then select: assistedGitHub Copilot assisted permissions generally available (2026-10-26) · Oct 2026 · source -
Enable assisted permissions in VS Code's Copilot permissions picker to reduce approval prompts during agentic tasks.
Open the permissions picker in VS Code > Select 'Assisted permissions'GitHub Copilot assisted permissions generally available (2026-10-26) · Oct 2026 · source
Package Firewall shipped suggested Sits between CI/CD runners and coding agents and upstream package registries to inspect metadata requests and downloads for malicious packages, check against the GitHub Advisory Database, perform supply-chain checks including attestation downgrades, and provide an exception-request workflow for erroneously blocked packages.
Suggested capability: Vulnerability database matching. This is our guess, not confirmed.
Also counts toward: CI/CD pipeline integration
release
- Currently supports npm packages through the firewall. GitHub package firewall in public preview (2026-10-20) · Oct 2026 · source · release history
- Introduces GitHub package firewall for GitHub Enterprise Cloud, sitting between endpoints (Actions runners, coding agents) and upstream package registries to inspect metadata requests and package downloads for malicious activity.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub package firewall in public preview (2026-10-20) · Oct 2026 · source · release history
- Performs supply-chain checks including attestation downgrades as a policy control. GitHub package firewall in public preview (2026-10-20) · Oct 2026 · source · release history
- Provides an exception request workflow for packages blocked erroneously, consistent with other GitHub Advanced Security flows. GitHub package firewall in public preview (2026-10-20) · Oct 2026 · source · release history
- Checks packages against the GitHub Advisory Database for malware or vulnerability alerts as a policy control. GitHub package firewall in public preview (2026-10-20) · Oct 2026 · source · release history
example
-
Route an Actions runner's npm traffic through the package firewall instead of pointing directly at the npm registry — blocks malicious packages at install time on CI/CD hosts.
In your GitHub Enterprise Cloud admin console, go to Settings > Package firewall, configure the cooldown period and advisory/attestation policies, then follow 'Protecting endpoints with package…GitHub package firewall in public preview (2026-10-20) · Oct 2026 · source
Agent Activity Monitoring shipped Captures and exposes agent activity data via OpenTelemetry for integration with existing enterprise monitoring tools.
release
-
Adds
repo.code_quality_findings_dismissedaudit log event, recording who dismissed one or more backlog Code Quality findings, when, the repository and rule, and the identifiers and count of affected findings.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Audit GitHub Code Quality finding dismissals and reopenings (2026-10-13) · Oct 2026 · source · release history -
Adds five independently controllable capture classes —
prompts,responses,toolArguments,toolOutput, andpolicyDetail— each off by default, available in Copilot CLI, the GitHub Copilot app, and VS Code sessions using Agent Host. Client telemetry user attribution and configurable capture (2026-10-12) · Oct 2026 · source · release history -
Retains
captureContentas a legacy shorthand covering all five content capture classes, but explicitly never enables identity capture. Client telemetry user attribution and configurable capture (2026-10-12) · Oct 2026 · source · release history -
Adds
telemetry.capture.identitysetting to attribute Copilot activity to a user, appendinguser.name,process.user.name, andhost.nameto OpenTelemetry data — off by default, separate from existing pseudonymous identifiers.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Client telemetry user attribution and configurable capture (2026-10-12) · Oct 2026 · source · release history - Adds OpenTelemetry support in the GitHub Copilot app to track agent activity in existing monitoring tools, configured through enterprise-managed settings. GitHub Copilot weekly releases — September 21 (2026-09-25) · Sep 2026 · source · release history
example
-
Enable user attribution plus tool-argument capture for an audit pipeline — without collecting prompts or responses — in your enterprise managed settings.
telemetry: capture: identity: true toolArguments: true prompts: false responses: false toolOutput: false policyDetail: falseClient telemetry user attribution and configurable capture (2026-10-12) · Oct 2026 · source
Repository Custom Property Governance shipped Allows administrators to control and suggest values for repository custom properties as part of governance policies.
release
- Port.io is the first partner integration for external custom properties, with a published integration guide for syncing business context to GitHub. Bring business context with external custom properties (2026-09-29) · Sep 2026 · source · release history
- Supports external custom properties everywhere standard custom properties work today, including repository views, repository filtering, and ruleset targeting. Bring business context with external custom properties (2026-09-29) · Sep 2026 · source · release history
- Adds external custom properties APIs, letting enterprise integrations push read-only repository metadata (ownership, service tier, lifecycle stage, compliance status) from an external system of record into GitHub under a dedicated namespace prefix.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Bring business context with external custom properties (2026-09-29) · Sep 2026 · source · release history
- Adds a Repository custom property suggestions Copilot policy at the enterprise and organization level to control whether Copilot suggests allowed values when creating custom property definitions.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub Copilot suggests custom properties definitions (2026-09-15) · Sep 2026 · source · release history
- GitHub Copilot now suggests relevant allowed values when admins create custom property definitions (single-select or multi-select) for repositories, speeding up governance taxonomy setup. GitHub Copilot suggests custom properties definitions (2026-09-15) · Sep 2026 · source · release history
example
-
Enable or restrict the new suggestion feature org-wide before rolling out custom property definitions to your repository fleet.
In your organization (or enterprise) settings, go to Copilot > Policies and set `Repository custom property suggestions` to Enabled or Disabled.GitHub Copilot suggests custom properties definitions (2026-09-15) · Sep 2026 · source
Execution Protection Policy API shipped Provides programmatic management of actor and event rules for execution protection at enterprise, organization, and repository levels.
Also counts toward: REST API
release
-
GitHub Actions now blocks
pull_request_targetevents by default in all public repositories via a new workflow execution protection rule, preventing fork-sourced untrusted code from accessing base-repository secrets.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ pull_request_target blocked by default December 2 (2026-11-02) · Nov 2026 · source · release history -
Starting December 2, 2026,
pull_request_targetworkflow runs in public repositories will be blocked by default and will fail unless an Actions event policy explicitly allows them. Brownout enforcement windows on November 9 (16:00–18:00 UTC) and November 16 (16:00–18:00 UTC) will surface affected workflows early. pull_request_target blocked by default December 2 (2026-11-02) · Nov 2026 · source · release history - Adds bulk import of all branch protection rules to rulesets via Settings → Rulesets → Import branch protection rules, with preview, enforcement-status selection (Active, Evaluate, or Disabled), and a choice to keep or delete the original rules after conversion.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Bulk migrate branch protections to rulesets for a repository (2026-10-20) · Oct 2026 · source · release history
- New REST API for Actions execution protections lets you create, read, update, and delete actor and event rules — including workflow path conditions — at the enterprise, organization, and repository level, enabling policy-as-code governance at scale.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Workflow execution protections in GitHub Actions generally available (2026-09-17) · Sep 2026 · source · release history
example
-
Migrate all branch protection rules to rulesets at once, previewing what will be created before committing.
1. Go to your repository's Settings → Rulesets. 2. Click 'Import branch protection rules'. 3.Bulk migrate branch protections to rulesets for a repository (2026-10-20) · Oct 2026 · source
Runner Version Lifecycle Management shipped Enforces minimum runner version requirements for self-hosted runners and provides an API to query registration and runtime deprecation dates, enabling automated fleet compliance monitoring.
Also counts toward: REST API
release
- Adds an Agentic autofix policy under Advanced Security policies for enterprise administrators to control access. Agentic autofix for code scanning alerts general availability (2026-10-15) · Oct 2026 · source · release history
- Introduces the Assign to Copilot button on individual code scanning alerts, replacing the previous Generate Fix option for eligible customers. Agentic autofix for code scanning alerts general availability (2026-10-15) · Oct 2026 · source · release history
-
Enables agentic autofix via the Update a Code Scanning Alert REST API by setting
assigneesto["copilot-swe-agent[bot]"]on alerts on the default branch.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Agentic autofix for code scanning alerts general availability (2026-10-15) · Oct 2026 · source · release history - Self-hosted runners below version 2.329.0 on GitHub Enterprise Cloud will not be able to register or reregister starting September 29, 2026; existing runners below the minimum runtime version will stop executing workflow jobs even if previously registered. Self-hosted runner version enforcement date has moved (2026-09-28) · Sep 2026 · source · release history
- Adds a REST API for runner version deprecations to query registration and runtime deprecation dates for any runner version and build automated alerts for fleets nearing their deadline.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Self-hosted runner version enforcement date has moved (2026-09-28) · Sep 2026 · source · release history
Evaluate Mode Availability shipped Makes evaluate (shadow) mode generally available, allowing administrators to run protection rules without blocking workflows.
release
- Review which workflow runs the default rule would block before enforcement by checking the Insights view while the rule runs in evaluate mode. pull_request_target blocked by default December 2 (2026-11-02) · Nov 2026 · source · release history
- After a successful proof-of-presence challenge, the verified session remains elevated for two hours in the same browser session, matching the existing sudo mode session model. Require proof of presence for high-impact actions (2026-09-24) · Sep 2026 · source · release history
- Supports two proof-of-presence requirement levels — re-authentication (password-level IdP sign-in) and MFA (authenticator app or biometric as configured in Entra ID) — allowing enterprises to set custom IdP policies governing which actions trigger which level.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Require proof of presence for high-impact actions (2026-09-24) · Sep 2026 · source · release history
- Evaluate mode (shadow mode) is now generally available, letting you run execution protection rules without blocking workflows and preview which runs would be affected before enforcement. Workflow execution protections in GitHub Actions generally available (2026-09-17) · Sep 2026 · source · release history
Execution Protection Insights shipped Provides visibility into how execution protection rules are evaluated and enforced across the organization, including shadow mode previews.
release
- Access updated code security and secret risk assessments that now show whether each finding is in a protected or unprotected repository, helping identify where to extend coverage — available to organization admins and security managers under the organization's Security tab > Assessments.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Security risk assessments include repository protection status (2026-11-02) · Nov 2026 · source · release history
-
Dismissal-request webhook payloads now include
exemption_request.number, the repository-scoped request number also available in the REST API, enabling correlation of bypass requests across integrations.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Updates to GitHub secret scanning (2026-10-20) · Oct 2026 · source · release history - Adds an Insights view to audit how execution protection actions evaluate and enforce rules across your enterprise, organization, and repositories — including in evaluate (shadow) mode before enforcement. Workflow execution protections in GitHub Actions generally available (2026-09-17) · Sep 2026 · source · release history
example
-
Identify unprotected repositories with active findings so you can prioritize where to extend branch protection or code security policies.
In your organization, go to Security > Assessments, then open the code security risk assessment or secret risk assessment — each finding now shows a 'protected' or 'unprotected' status for its…Security risk assessments include repository protection status (2026-11-02) · Nov 2026 · source
Agentic Workflow Authoring shipped Lets users define automations in natural language Markdown files that compile to standard GitHub Actions YAML, runnable inside Actions with existing runner groups, policies, and prebuilt templates.
Also counts toward: CI/CD pipeline integration, Command-line interface
release
- GitHub adds Agentic Workflows, letting you define automation in natural language Markdown files that compile to standard Actions YAML and run inside GitHub Actions with existing runner groups and policies. GitHub Agentic Workflows generally available (2026-10-28) · Oct 2026 · source · release history
-
Add new workflow templates to a repository using
gh aw add-wizard. GitHub Agentic Workflows generally available (2026-10-28) · Oct 2026 · source · release history - Run agentic workflows on self-hosted Actions Runner Controller runners with Docker-in-Docker support.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub Agentic Workflows generally available (2026-10-28) · Oct 2026 · source · release history
example
-
Bootstrap a new agentic workflow from a prebuilt template — such as triage or dependency management — without writing Actions YAML by hand.
gh aw add-wizardGitHub Agentic Workflows generally available (2026-10-28) · Oct 2026 · source
Copilot Fusion Automatic Model Routing shipped Automatically routes requests between on-device and cloud models across Copilot CLI, VS Code, the Copilot app, and JetBrains IDEs without requiring users to manually switch models per request.
Also counts toward: Command-line interface
release
-
GitHub Copilot Fusion now routes requests between eligible on-device and cloud models in Copilot CLI, the Copilot app, and VS Code without requiring manual model switching per request.
GitHub Copilot Fusion now supports selection of local models (2026-10-28) · Oct 2026
· source
· release history
-
Enable local model routing in VS Code by setting
chat.copilot.localModel.enabled, then select Standard in Copilot Fusion to let Copilot choose between local and cloud models automatically.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub Copilot Fusion now supports selection of local models (2026-10-28) · Oct 2026 · source · release history -
Users on paid Copilot plans receive a 30% discount on model costs when using Copilot Fusion for a limited time.
Route and orchestrate models with GitHub Copilot Fusion (2026-10-28) · Oct 2026
· source
· release history
- Copilot Fusion is available in Visual Studio Code, the GitHub Copilot app, GitHub Copilot CLI, and JetBrains IDEs on all Copilot plans. Route and orchestrate models with GitHub Copilot Fusion (2026-10-28) · Oct 2026 · source · release history
Copilot Image Generation shipped Generates and edits images from natural language prompts within Copilot chat sessions in VS Code, the Copilot app, and Copilot CLI, with inline preview, workspace saving, optional AI watermarking, and organization-level disable controls.
Also counts toward: Command-line interface, Natural-language query
release
-
GitHub Copilot chat now supports image generation and editing using natural language.
GitHub Copilot app, Universe releases (2026-10-28) · Oct 2026
· source
· release history
- Generate and edit images using natural language in any Copilot chat session in VS Code, the GitHub Copilot app, or Copilot CLI; results preview inline and save directly to your workspace.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Generate and edit images directly in Copilot (2026-10-28) · Oct 2026 · source · release history
- Opt in to a visible Made with AI watermark on Copilot-generated and edited images; watermarking is off by default. Generate and edit images directly in Copilot (2026-10-28) · Oct 2026 · source · release history
example
-
Disable image generation for your organization to prevent AI-generated images from being produced by Copilot users.
In GitHub: go to Organization Settings > Copilot > Policies > Model policies, then disable the image generation model.Generate and edit images directly in Copilot (2026-10-28) · Oct 2026 · source
GitHub Security Extension shipped Provides a Copilot plugin that enables browsing and querying code scanning alerts directly in the Copilot app or CLI, governed by existing tool permission settings, available in public preview on github.com and GitHub Enterprise Cloud.
Also counts toward: Command-line interface, Natural-language query, Plugin system
release
-
Ask Copilot about alerts in chat using the security extension's tools, governed by your existing tool permission settings.
Security extension for the GitHub Copilot app (2026-10-28) · Oct 2026
· source
· release history
-
Install the security extension with
copilot plugin install github-security@awesome-copilotin the terminal, or search forgithub-securityin the Copilot app's Customize panel and click Install.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Security extension for the GitHub Copilot app (2026-10-28) · Oct 2026 · source · release history - The security extension is available in public preview on github.com and GitHub Enterprise Cloud with data residency; GitHub Enterprise Server is not supported. Security extension for the GitHub Copilot app (2026-10-28) · Oct 2026 · source · release history
example
-
Install the GitHub security extension from the terminal so you can immediately browse code scanning alerts in the Copilot app.
copilot plugin install github-security@awesome-copilotSecurity extension for the GitHub Copilot app (2026-10-28) · Oct 2026 · source
Managed Plugin Governance shipped Allows repository maintainers to define default plugins and a plugin marketplace for contributors, while giving enterprise administrators controls to require, block, or restrict plugins to approved marketplaces across the organization.
Also counts toward: Extension marketplace, Plugin system
release
- Repository maintainers can now define default plugins and a plugin marketplace so contributors get consistent Copilot plugin setup without repeating configuration per project.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Repository plugin defaults and enterprise plugin controls generally available (2026-10-28) · Oct 2026 · source · release history
- Managed plugin controls are available on GitHub Enterprise Cloud for Copilot Business and Copilot Enterprise license holders; repository defaults are available to individual Copilot users as well. Repository plugin defaults and enterprise plugin controls generally available (2026-10-28) · Oct 2026 · source · release history
- Contributors can turn off repository-default plugins where enterprise policy permits. Repository plugin defaults and enterprise plugin controls generally available (2026-10-28) · Oct 2026 · source · release history
- Enterprise administrators can now require plugins (auto-installed and user-locked), block plugins, and restrict installation to approved marketplaces through managed settings that override repository and personal choices. Repository plugin defaults and enterprise plugin controls generally available (2026-10-28) · Oct 2026 · source · release history
Enforcement Policy Hierarchy shipped Enables organization and repository owners to enforce security settings that prevent enterprise administrators from overriding them.
release
- Every commit pushed to a repository now has a durable, authenticated pusher identity attached to it, independent of author and committer metadata. Push attribution for commits in limited public preview (2026-10-12) · Oct 2026 · source · release history
- Adds a new repository rule condition, Committer must match pusher, that blocks pushes where the committer metadata does not match any verified email address of the authenticated pusher.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Push attribution for commits in limited public preview (2026-10-12) · Oct 2026 · source · release history
- Surfaces the authenticated pusher identity in the UI and API alongside the existing author and committer fields, enabling spot-checks of suspicious activity and faster security investigations. Push attribution for commits in limited public preview (2026-10-12) · Oct 2026 · source · release history
- Adds Enforce for repository and organization owners option to the Enforcement dropdown in security configurations, blocking organization administrators from overriding enterprise-level GitHub Advanced Security settings.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Enforce GitHub Advanced Security configurations (2026-09-15) · Sep 2026 · source · release history
Pull Request Archiving shipped Allows users with triage, write, maintain, or admin roles to archive pull requests, making them fully read-only (blocking all comments, reactions, and automated activity) and hidden from public view while remaining visible to administrators.
Also counts toward: Role-based access control
release
- Archiving a pull request now blocks all new activity (comments, reactions, automated comments) for every role including admins — previously admins could still comment on a locked/archived PR. Triage role users or higher can now archive pull requests (2026-10-08) · Oct 2026 · source · release history
- Archived pull requests are hidden from public view but remain visible to repository administrators. Triage role users or higher can now archive pull requests (2026-10-08) · Oct 2026 · source · release history
- Archiving a pull request now makes its conversation fully read-only: new comments, reactions, and automated comments are blocked for all users, including admins. Triage role users or higher can now archive pull requests (2026-10-08) · Oct 2026 · source · release history
- Extends pull request archive and unarchive permissions to users with the triage, write, maintain, or admin role — previously only admins could archive.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Triage role users or higher can now archive pull requests (2026-10-08) · Oct 2026 · source · release history
APM Dependency Updates shipped Extends Dependabot to open pull requests that update git dependencies declared in Agent Package Manager configuration files, keeping AI agent skills, prompts, and instructions current.
release
- Dependabot now supports version updates for Agent Package Manager (APM) dependencies — covering AI agent skills, prompts, and instructions — available on github.com for all GitHub plans and in GitHub Enterprise Server 3.24. Dependabot version updates support Agent Package Manager (2026-11-03) · Nov 2026 · source · release history
-
Add an
apmentry to.github/dependabot.yml, specifying the directory containingapm.ymland an update schedule, to have Dependabot open pull requests updating git dependencies declared inapm.ymland regeneratingapm.lock.yamlwhen present.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Dependabot version updates support Agent Package Manager (2026-11-03) · Nov 2026 · source · release history
example
-
Keep AI agent skills and prompts current by having Dependabot open PRs for outdated APM git dependencies on a weekly schedule.
version: 2 updates: - package-ecosystem: "apm" directory: "/" schedule: interval: "weekly"Dependabot version updates support Agent Package Manager (2026-11-03) · Nov 2026 · source
Workflow File Targeting shipped Allows execution protection rules to be scoped to specific workflow files rather than the entire repository.
release
-
Use workflow file targeting inside an Actions event policy to explicitly allow
pull_request_targetfor specific workflows rather than the entire repository. pull_request_target blocked by default December 2 (2026-11-02) · Nov 2026 · source · release history - Supports gradual onboarding: individual workflows can be opted in, after which GitHub Actions enforces that every dependency of that workflow has a lockfile entry and runs its recorded commit. GitHub Actions workflow lockfiles in public preview (2026-10-14) · Oct 2026 · source · release history
-
Adds workflow file targeting to scope execution protection rules to specific workflow files (e.g.
deploy.yml) rather than an entire repository, so different policies can apply to different workflows in the same repo. Workflow execution protections in GitHub Actions generally available (2026-09-17) · Sep 2026 · source · release history
Webhook IP Range Updates shipped Adds three new CIDR prefixes to the Meta API's webhook IP ranges, requiring administrators to update static network allowlists to accept incoming webhook deliveries from the new addresses.
release
-
The Meta API's
hooksfield now includes three new CIDR prefixes —9.234.98.160/28,9.234.98.176/28, and9.234.106.48/28— covering all github.com plans including GitHub Enterprise Cloud.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Webhook IP ranges added to the Meta API (2026-10-29) · Oct 2026 · source · release history -
Static network allowlists for incoming webhook deliveries will reject traffic from
9.234.98.160/28,9.234.98.176/28, and9.234.106.48/28unless those CIDR prefixes are added manually. Webhook IP ranges added to the Meta API (2026-10-29) · Oct 2026 · source · release history
example
-
Pull the current webhook IP ranges from the Meta API to update a static network allowlist before the new CIDRs go live.
curl -s https://api.github.com/meta | jq '.hooks'Webhook IP ranges added to the Meta API (2026-10-29) · Oct 2026 · source
Image Asset Management shipped Provides mechanisms to upload local files and embed them inline in Markdown, and automatically rewrite local image paths to uploaded asset URLs while preserving alt text.
release
- Opt in to a visible Made with AI watermark on Copilot-generated and edited images; watermarking is off by default. Generate and edit images directly in Copilot (2026-10-28) · Oct 2026 · source · release history
-
Rewrites local image paths already present in the Markdown body (e.g. ) to the uploaded asset URL, preserving existing alt text; unreferenced attachments are appended at the end. GitHub CLI: Media in issues, pull requests, and comments (2026-09-01) · Sep 2026
· source
· release history
docs
- Attaching files with GitHub CLI Attach local images and videos to issues, pull requests, and comments without leaving the command line. docs update · Sep 2026 · source
Automated Code Review Approval shipped Enables the cyber tool to automatically review code changes and submit formal approvals in pull requests that count toward required-approvals rules, with configurable dismissal of prior approvals when new commits are pushed.
release
- Supports bulk remediation of up to 25 alerts at once from the security alerts list or a security campaign, consolidated into a single pull request. Agentic autofix for code scanning alerts general availability (2026-10-15) · Oct 2026 · source · release history
- Copilot's approval is automatically dismissed when new commits are pushed after approval, matching human-reviewer dismissal behavior, and a fresh review can be requested to re-approve. Copilot code review can now approve pull requests (2026-09-01) · Sep 2026 · source · release history
- Enables Copilot to submit a formal PR approval that counts toward a repository's required-approvals rule when turned on by an admin — off by default, configurable at enterprise, organization, and repository level, including per-file-path controls at the repository level. Copilot code review can now approve pull requests (2026-09-01) · Sep 2026 · source · release history
AI Push Protection shipped Checks pushes for unstructured credentials before secrets enter repository history, with spending caps for AI-powered checks, available in private preview for GitHub Enterprise Cloud and GitHub Teams.
release
-
Expands push protection defaults to block commits containing
anthropic_service_api_keyandanthropic_user_api_keyon all repositories with secret scanning enabled, including free public repositories. Secret scanning blocks Anthropic keys by default, adds Salesforce (2026-10-13) · Oct 2026 · source · release history - Adds AI push protection that checks for unstructured credentials at push time, before a secret enters repository history, available in private preview for GitHub Enterprise Cloud and GitHub Teams with GHSP or GHAS. Purpose-built model for leaked secret detection (2026-10-07) · Oct 2026 · source · release history
example
-
Cap spending on AI push protection and secret-classifier checks before opting into the public preview.
In the GitHub UI: Billing and licensing > Budgets and alerts > New budget > SKU-level budget > Product: Advanced Security > SKU: Secret Protection AI Credits > Enable 'Stop usage when budget limit is…Purpose-built model for leaked secret detection (2026-10-07) · Oct 2026 · source
Automated Commit Message Generation shipped Generates descriptive commit messages for autofix suggestions and automated code fixes during the review process.
release
-
Generates a commit title and optional description automatically when you commit an eligible batch of Copilot code review suggestions, including batches that mix in non-Copilot comments.
Copilot code review: An improved review experience (2026-09-18) · Sep 2026
· source
· release history
-
Copilot code review now resolves addressed comments during subsequent reviews, suggests commit messages when applying code suggestions, supports shell tools to validate changes, and combines findings from multiple agents in Lite reviews.
GitHub Copilot weekly releases — September 14 (2026-09-18) · Sep 2026
· source
· release history
- Generates smart commit messages when you apply a Copilot code review autofix suggestion, replacing the generic auto-filled message with one describing the specific change.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Auto-resolution and analysis updates in Copilot code review (2026-09-11) · Sep 2026 · source · release history
Migration Support shipped Supports near-zero-downtime repository migrations from GitHub Enterprise Server to GitHub Enterprise Cloud with Data Residency, including live migrations and compatibility checks for older GHES versions.
release
-
Supports migrations from GHES versions 3.17.18+, 3.18.12+, 3.19.9+, 3.20.3+, 3.21.3+, and 3.22.0+.
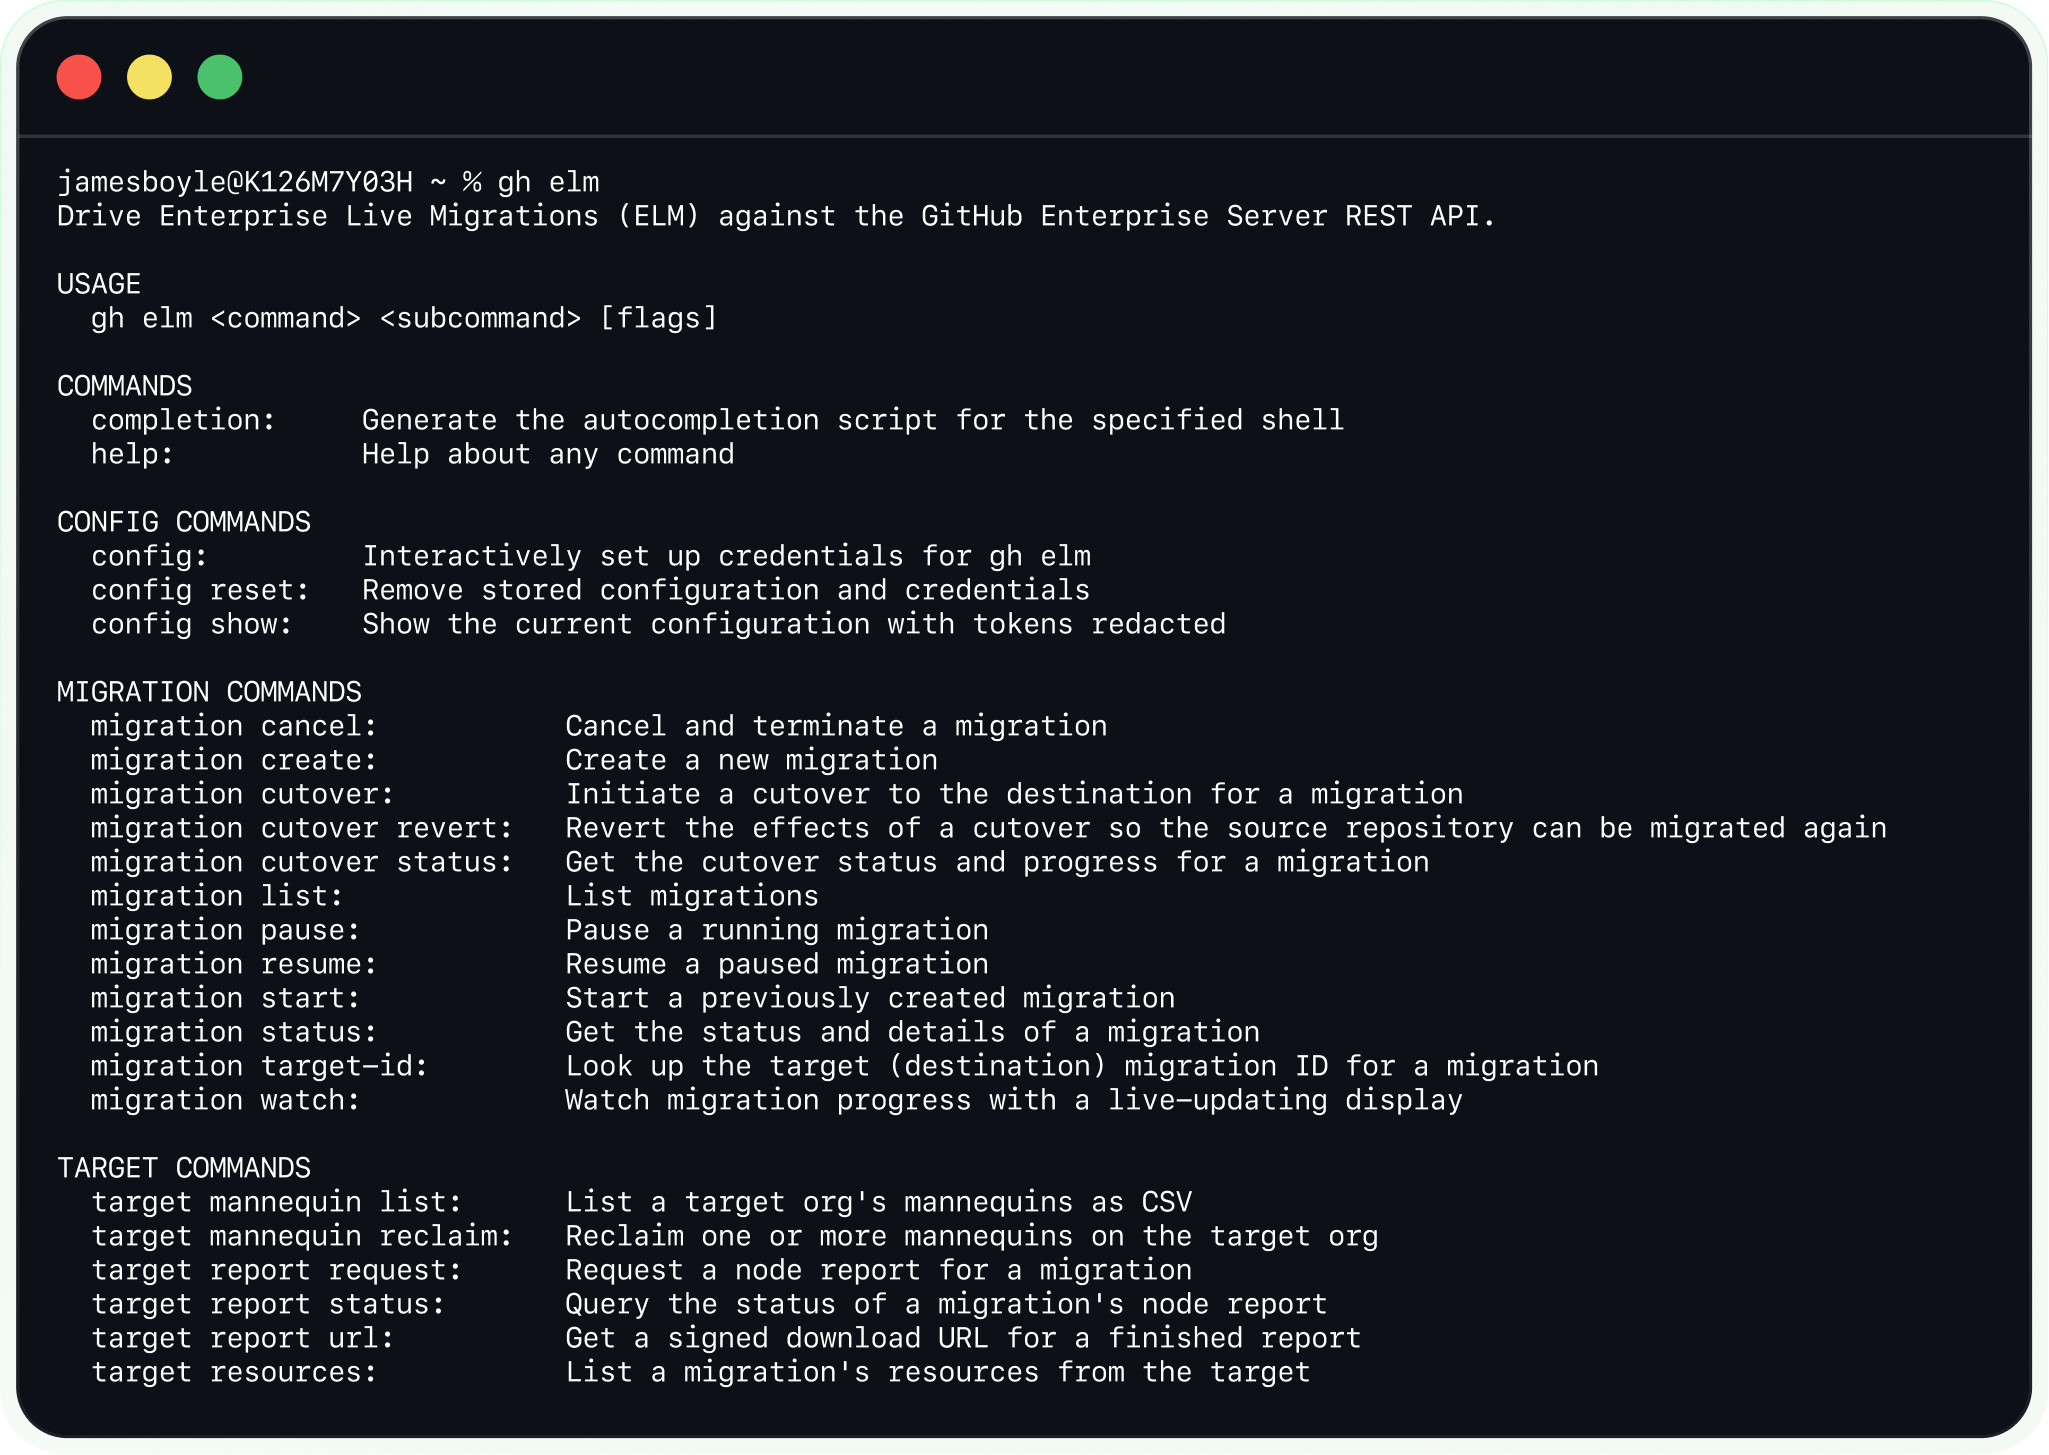 Enterprise Live Migrations from GHES to ghe.com generally available (2026-09-01) · Sep 2026
· source
· release history
- Introduces Enterprise Live Migrations (ELM) as a generally available service running on GHES appliances for near-zero-downtime repository migrations from GHES to GitHub Enterprise Cloud with Data Residency (GHEC DR). Enterprise Live Migrations from GHES to ghe.com generally available (2026-09-01) · Sep 2026 · source · release history
- ELM and GitHub Enterprise Importer (GEI) can be run concurrently as part of the same migration strategy, letting teams choose the right tool per repository. Enterprise Live Migrations from GHES to ghe.com generally available (2026-09-01) · Sep 2026 · source · release history
GitHub Actions CFG Modernization shipped Migrates the GitHub Actions control flow graph to the shared CFG library, replacing legacy Completion classes with new edge label types, which may require updates to custom CFG-dependent queries.
release
-
The legacy Completion classes have been removed from the GitHub Actions CFG; use CFG edge labels
DirectSuccessor,BooleanSuccessor, andReturnSuccessorinstead. CodeQL 2.27.3 adds Python 3.15 features and JSON data extensions (2026-11-03) · Nov 2026 · source · release history - The GitHub Actions control flow graph (CFG) now uses the shared CFG library; custom queries that rely on specific CFG nodes, edges, or basic block boundaries may need updates. CodeQL 2.27.3 adds Python 3.15 features and JSON data extensions (2026-11-03) · Nov 2026 · source · release history
Copilot Dreaming shipped Continuously refines repository memories and personal preferences in the background, proposing updates to instruction files and repository skills via pull requests.
release
- Copilot Dreaming is now in public preview — opt in through Copilot settings (individuals) or Copilot policies (organizations and enterprises) — letting Copilot reflect on past sessions to update personal memories, propose changes to repository skills and custom instruction files via pull requests, and turn recurring… GitHub intelligence puts your code, context, and history to work (2026-10-28) · Oct 2026 · source · release history
example
-
Enable Copilot Dreaming for your organization so agents continuously refine repository memories and propose instruction updates via pull requests.
In GitHub, go to Organization Settings > Copilot > Policies, then enable 'Dreaming' to allow agents to update memories and propose skill and custom instruction file changes in pull requests.GitHub intelligence puts your code, context, and history to work (2026-10-28) · Oct 2026 · source
Copilot Projects shipped Provides a multi-repository, multi-session workspace in the Copilot app that coordinates multiple agents running in parallel and surfaces results such as pull requests for review.
release
-
GitHub Copilot Projects now support automations for repeatable tasks, such as triggering a workflow whenever a specific event occurs.
GitHub Copilot app, Universe releases (2026-10-28) · Oct 2026
· source
· release history
- GitHub Copilot app now supports Projects, a workspace that spans multiple repositories and sessions, coordinating multiple agents in parallel and returning results such as pull requests for review — now in public preview. GitHub Copilot app, Universe releases (2026-10-28) · Oct 2026 · source · release history
Copilot SDK Workload Identity for GitHub Apps shipped Allows GitHub Apps to authenticate against the Copilot SDK using server-to-server installation access tokens and a scoped read-only Copilot Requests permission, enabling agents and automated services to call Copilot as a workload identity rather than on behalf of a user.
release
- Introduces a read-only Copilot Requests organization permission for GitHub Apps, scoping what an app can do when authenticating as a workload identity against the Copilot SDK. GitHub Copilot supports server-to-server authentication (2026-10-27) · Oct 2026 · source · release history
- Adds server-to-server authentication (public preview) for GitHub Apps installed on organizations, enabling agents and automated services to call the Copilot SDK using a short-lived installation access token instead of a user's credentials.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub Copilot supports server-to-server authentication (2026-10-27) · Oct 2026 · source · release history
Local Sandbox Execution shipped Limits the agent's access to files, networks, and credentials by running tasks in a local sandbox environment.
release
-
Introduces local sandboxing — now generally available in Copilot CLI, the Copilot app, and VS Code sessions using Agent Host — to limit agents' access to files, networks, and credentials at no extra cost.
GitHub Copilot weekly releases — October 5 (2026-10-09) · Oct 2026
· source
· release history
- Adds local sandboxing in the GitHub Copilot app (public preview) to limit agents' access to files, networks, and credentials.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub Copilot weekly releases — September 21 (2026-09-25) · Sep 2026 · source · release history
npm Trusted Publishing Event Restrictions shipped Rejects trusted publishing tokens issued from GitHub Actions `issue_comment` events, requiring workflows to use permitted events such as `push`, `release`, or `workflow_dispatch`.
release
-
Trusted publishing tokens issued from GitHub Actions
issue_commentevents are now rejected by npm; workflows that publish onissue_commentmust be moved to a permitted event (push,release, orworkflow_dispatch). Unvalidated npm trusted publishing configurations now expire (2026-10-02) · Oct 2026 · source · release history -
npm now rejects trusted publishing tokens from GitHub Actions
issue_commentevents; move publishing topush,release, orworkflow_dispatchinstead. Unvalidated npm trusted publishing configurations now expire (2026-10-02) · Oct 2026 · source · release history
Issue Form Field Validation shipped Allows maintainers to enforce a minimum character length on individual issue form fields to require a minimum level of detail from submitters.
release
-
Adds support for customizing the submission form via
.github/VULNERABILITY_REPORT.ymlusing issue form syntax withmin_lengthvalidation. Structured forms for private vulnerability reports (2026-10-01) · Oct 2026 · source · release history -
Form fields support
min_length(issue form syntax) so maintainers can enforce a minimum level of detail per field. Structured forms for private vulnerability reports (2026-10-01) · Oct 2026 · source · release history
Cloud Sandbox Integration shipped Integrates a high-performance cloud execution environment directly into the unified agent interface.
release
-
Adds enterprise policy diagnostics to verify that Copilot policies are correctly detected and enforced on a device.
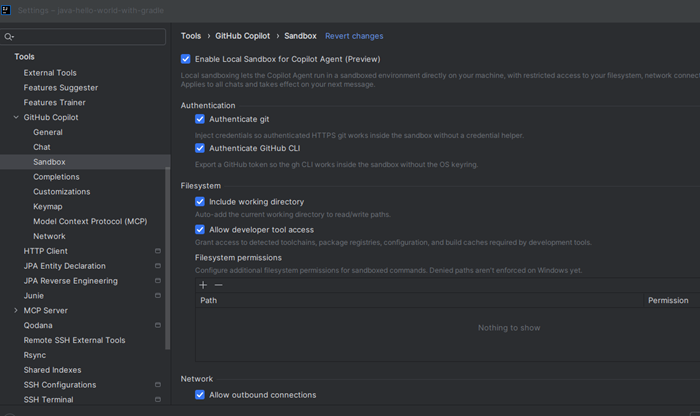 Enterprise-managed sandbox in Copilot for JetBrains (2026-09-09) · Sep 2026
· source
· release history
- Cloud agent gains Sandbox to provide a faster cloud execution environment in the unified experience. Upcoming changes to GitHub Copilot policies and billing (2026-08-28) · Aug 2026 · source · release history
Content Exclusion Policy Enforcement shipped Ensures that content exclusion policies set by administrators are honored in agentic workflows and the unified agent experience, preventing excluded files from being used as context.
Also counts toward: Command-line interface
release
- Copilot app and CLI now honor content exclusions, keeping sensitive code out of context across agentic workflows. GitHub Copilot weekly releases — August 31 (2026-09-04) · Sep 2026 · source · release history
- Copilot app and Copilot CLI now respect content exclusion policies set by enterprise, organization, and repository administrators, preventing excluded files from being used as context in agentic workflows. Content exclusions generally available in Copilot app and CLI (2026-09-02) · Sep 2026 · source · release history
Dependabot Python 3.15 Support shipped Adds Python 3.15 compatibility to Dependabot version updates, available to all github.com users and in GitHub Enterprise Server 3.24.
Also counts toward: Scripting language support
release
- Dependabot now supports Python 3.15, available to all github.com users and included in GitHub Enterprise Server 3.24.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ Dependabot now supports Python 3.15 (2026-11-03) · Nov 2026 · source · release history
Copilot Memory shipped Remembers personal preferences and repository conventions across sessions in the Copilot app, CLI, VS Code, cloud agent, code review, Slack, Teams, and GitHub Mobile on paid plans.
release
- GitHub Copilot Memory is now generally available on paid Copilot plans, letting Copilot remember personal preferences and repository conventions across sessions in the Copilot app, Copilot CLI, VS Code, Copilot cloud agent, Copilot code review, Slack, Teams, and GitHub Mobile. GitHub intelligence puts your code, context, and history to work (2026-10-28) · Oct 2026 · source · release history
Copilot Standalone Plan shipped Provides Copilot access for users in an enterprise account without a GitHub Enterprise license at $10 per user per month, delivering the same features and models as Copilot Enterprise but without monthly AI credits per seat.
release
- Users in an enterprise account without a GitHub Enterprise license get Copilot access through Copilot Standalone at $10 per user per month, with the same features and models as Copilot Enterprise but no monthly AI credits per seat. GitHub Enterprise now includes access to GitHub Copilot (2026-10-28) · Oct 2026 · source · release history
Cross-Repository Code Search shipped Allows users to search for exact text, symbols, regex patterns, or natural-language descriptions across multiple repositories without a local clone, narrowing results by repository, path, or language.
Also counts toward: Natural-language query
release
-
Use
/researchin Copilot to search for exact text, symbols, regex patterns, or natural-language descriptions across multiple repositories without a local clone, narrowing results by repository, path, or language.︀︄︇︀︅︉︀︅︀︀︃︀︀︅︅︀︅︊︀︄︆︀︃︄ GitHub intelligence puts your code, context, and history to work (2026-10-28) · Oct 2026 · source · release history
Multi-Model Comparison shipped Runs multiple models and harnesses in parallel in the Agents window, displays results side by side, and lets users request a Judge model recommendation or synthesize outputs from multiple models.
release
-
Run models and harnesses in parallel in the Agents window, review results side by side, ask a Judge model to recommend a solution, or choose Synthesize to combine ideas — model comparison is in preview.
GitHub Copilot in VS Code, Universe releases (2026-10-28) · Oct 2026
· source
· release history
App-Attributed Copilot Usage Controls shipped Attributes Copilot usage driven by GitHub Apps to the installing organization, applying that organization's model policies, budgets, and spending controls, with app traffic identifiable in AI usage CSV reports via the app_client_id field.
release
-
Attributes app-driven Copilot usage to the installing organization — including model policies, budgets, and spending controls — with app traffic identifiable in AI usage CSV reports via the
app_client_idfield. GitHub Copilot supports server-to-server authentication (2026-10-27) · Oct 2026 · source · release history
Code Review Execution Context shipped Extends code review capabilities to execute shell commands, build artifacts, and run tests within the agent's sandbox environment.
release
- Expands Copilot code review analysis to use the full set of shell tools from the Copilot SDK — including running build commands, tests, and targeted scripts — behind the Copilot agent firewall. Auto-resolution and analysis updates in Copilot code review (2026-09-11) · Sep 2026 · source · release history
Chat Session Organization shipped Organizes related chat sessions into a hierarchy within the IDE interface and surfaces which sessions require user attention.
release
- Chat sessions in VS Code organize related chats into a hierarchy and surface which ones need attention. GitHub Copilot weekly releases — August 31 (2026-09-04) · Sep 2026 · source · release history
Code Coverage Merge Protection documented Prevents pull requests from being merged when uploaded code coverage falls below configured thresholds.
docs
- Prevent pull requests from being merged when uploaded code coverage falls below the levels your team requires. seen Oct 2026 · source
Lines in monospace are the tool's own words: help text
parsed from its source, or an endpoint from its API document. Under
release, a line is our summary of a dated release. Under
docs, it is quoted from the tool's own documentation or
website. Each links back to the source it came from.
Command line
20 commands for GitHub, each with where it came from. This tool has no source analysis yet, so there is no option reference and no captured run beside them.
No command matches.
Screenshots
From the release notes, newest first. Click one to see it full size.Media
Videos from the release notes, newest first. They play right here.Score card
-
Shipping velocity releases a month, last 12 months
-
Documentation quality release-notes rubric, 0–100
-
Breaking-change discipline how rarely a release breaks users, and notice given
-
Maintenance risk quiet time against its own cadence, maintainers
-
Innovation & surface new capabilities, API and MCP surface
Five scores for GitHub, each built from the releases, notes and API history this site tracks — and, on Researcher and Business, where it stands among every measured tool in its category and how that has moved.
Score cards are part of every paid plan.
See plans → Already subscribed? Sign in →Trajectory
Blank means never measured; nothing here is a filled-in zero.
Peer standings are included with Researcher and Business. See how this tool ranks against its competitors, using data we don't publish anywhere else.
See plans →Each score is 0–100 on a published rubric, derived from data this site already shows. A dimension we cannot measure says so — it is never scored 0 and never enters a rank.
How this is scored
- Shipping velocity — releases a month over the last 12 months, on a log scale where 16 a month scores 100. Needs 3 releases in the window.
- Documentation quality — the release-notes rubric published on the analytics page, unchanged.
- Breaking-change discipline — the share of releases carrying a breaking change (none scores 100, half or more scores 0). Only projects that label breaking changes are measured: a clean record cannot be told from an unlabelled one.
- Maintenance risk — quiet time measured against the tool's own release cadence (quiet longer than 90 days and three typical gaps scores 0), plus the number of active maintainers and whether contributors are growing, where known. Higher is lower risk.
- Innovation & surface — new capabilities in the feature ledger this year, API and MCP operations added, and the share of commits that are features: the mean of whichever we hold.
- Community health (open-source tools only) — each is a direction, not a size: contributors this year against last, the bus factor now against a year ago, and issues closed per issue opened, where steady scores 50, doubled 100 and halved 0; plus the median time to a maintainer's first reply (an hour scores about 100, a month or more 0). A commercial card has no repository and carries none of the four.
- Documented delivery (commercial tools) — when a vendor's documented new capabilities have slowed against its own baseline, that counts against the overall standing as heavily as two low dimensions. Steady delivery, or too little history to judge, leaves the standing alone; it is never a sixth score.
- Open-source tools are scored on repository signals; commercial tools on their published changelog. Ranks compare tools within one category and one profile and need at least five measured peers; the overall standing needs three ranked dimensions. Best-in-breed or consolidator is a shape, not a quality, and is never scored.
Release-note detail over time
See how much detail GitHub puts in its release notes, quarter by quarter, and compare it with tracked tools in the same category. This history uses up to ten retained, reviewed notes per tool; sparse or blank older quarters may reflect that limit.
Checking release-note history…
Website history
github.blog, every changeGitHub's home page and 40 more pages as they looked each month from September 2021 to October 2026: 188 renders, 87 changes of tagline or palette. Step through them, play them, or put any two months side by side.
Website history is included with Researcher and Business.
See plans → Already subscribed? Sign in →← → or h l a month · Shift a year · [ ] previous / next change · Space play · 1 2 3 page · T whole page · C compare · F full size
← → or h l the right month · Shift the left · S swap · W wipe · T whole page · Esc back
Rebranding timeline
Dates bound when a change appeared between captures. Possible rebrands are AI suggestions; a redesign alone does not establish a rebrand.
Coverage
Missing something? Tell us
What GitHub connects to, runs on and detects, read from its release notes and docs. So far: 7 new supported platforms, 4 updated detections, 4 new detections, 1 new integration, 1 retired supported platform.
17 changes, tracked since Oct 5, 2026.
-
Nov 32026
new GitHub Copilot integration in JetBrains Air
With Agent Client Protocol (ACP)
You can now delegate coding tasks, guide execution, and review results with GitHub Copilot in JetBrains Air. The integration uses the Agent Client Protocol (ACP) and supports tasks in your JetBrains IDE or in the cloud.
-
Nov 32026
new Cloud task execution via Air Teams in isolated Docker containers
Run Copilot in isolated cloud environments through Air Teams, from your IDE or browser. Tasks use your Copilot plan rather than JetBrains AI credits.
-
Nov 32026
new Python 3.15 syntax support
With unary plus in match literal patterns, Unicode 17 identifiers, frozendict, sentinel
The Python extractor now supports Python 3.15 syntax, including unary plus in match literal patterns and Unicode 17 identifiers. We've added support for the new frozendict and sentinel builtins introduced in Python 3.15, including data flow modeling for frozendict construction.
-
Nov 32026
new C23 bit-precise integer support
With _BitInt(N)
We've added support for C23 bit-precise integers ( _BitInt(N) ).
-
Nov 32026
updated BlazingMQ flow summaries for C/C++
With BloombergLP::bmqa::Message
We've added flow summaries for the BlazingMQ BloombergLP::bmqa::Message and MessageProperties classes and their iterators.
-
Nov 32026
updated Grape::API remote flow sources for Ruby
Adds body.read, body.string, params, GET, POST, cookies, env, query_string and 1 more. 9 in all.
CodeQL now treats Grape::API request sub-accessors as remote flow sources. These include body.read , body.string , params , GET , POST , cookies , env , query_string , and path_info .
-
Nov 32026
updated Python XXE, XML-bomb, and NoSQL injection queries respect threat model and data extensions
With py/xxe, py/xml-bomb, py/nosql-injection
The py/xxe , py/xml-bomb , and py/nosql-injection queries now respect your configured threat model when selecting untrusted data sources. By default, they still use remote flow sources. These queries now also include sources you model with data extensions.
-
Nov 32026
updated Java SSRF and URL-redirection queries recognize case-insensitive URI host comparisons
With java/unvalidated-url-redirection, URI.getHost()
The java/ssrf and java/unvalidated-url-redirection queries now recognize case-insensitive comparisons of URI.getHost() with fixed allowlist entries. They also recognize these checks when code stores the host in a local variable, which reduces false positives.
-
Nov 32026
new Python 3.15 support for Dependabot
You can now upgrade your projects to Python 3.15 and keep receiving Dependabot updates. Support for Python 3.15 is available to all github.com users and will be included in GitHub Enterprise Server 3.24.
-
Oct 222026
new Public monitoring for secret scanning in GHEC DR
With public commits, github.com
Public monitoring extends secret scanning beyond internal repositories by monitoring public commits across github.com, attributing exposed credentials back to your enterprise in real time.
-
Oct 202026
new npm 12, pnpm 11, pnpm 12, and Bun 1.4 support in Dependabot
You can now upgrade your projects to npm 12, pnpm 11 or 12, or Bun 1.4 and keep receiving Dependabot updates.
-
Oct 162026
new Xcode 27 runner image (GA)
With xcode-27-xlarge, macOS 27, Apple Silicon (arm64)
You can now use the generally available Xcode 27 runner image to build and test your Apple applications in GitHub Actions. Previously in public preview, this GitHub-hosted image runs on macOS 27 and includes the Xcode 27 toolchain and Apple SDKs.
-
Oct 152026
new AI Scan language and framework coverage
With PHP, Shell/Bash, Terraform configuration (HCL), Dockerfiles, JSP for Java, Blazor for C#
It complements CodeQL by finding vulnerabilities in pull request changes for languages and frameworks that CodeQL does not currently cover, including PHP, Shell/Bash, Terraform configuration (HCL), Dockerfiles, JSP for Java, Blazor for C#, and more.
-
Oct 102026
retired JetBrains IDE 2025.1 support ended
GitHub Copilot has ended support for JetBrains IDE 2025.1. You now need JetBrains IDE 2025.2 or later to use the plugin.
-
Oct 52026
new Lovable Labs secret scanning partner and detector
With lovable_api_key
Provider Secret type Lovable Labs lovable_api_key
-
Oct 52026
new Pydantic Services Inc. secret detectors
With logfire_token, pydantic_ai_gateway_api_key
Pydantic Services Inc. logfire_token Pydantic Services Inc. pydantic_ai_gateway_api_key
-
Oct 52026
new Supabase secret detectors
With supabase_oauth_access_token, supabase_scoped_personal_access_token
Supabase supabase_oauth_access_token Supabase supabase_scoped_personal_access_token
Editors & IDEs 3
SIEM & security analytics 1
Containers & orchestration 2
Chat & collaboration 1
Operating systems 1
Languages & runtimes 13
Hardware & accelerators 1
Other 1
Coding agents 2
Agent frameworks & SDKs 1
Nothing first seen in this window. That doesn't mean GitHub shipped nothing, only that we found no record of it.
How we count
Read from 73 of 223 release notes and docs updates we hold for GitHub. "First seen" is the earliest note that names something; "last" is the latest. Our history may start partway through GitHub's life, so an old integration can show a recent first-seen date.
Each change counts once: "added 40 checks" is one line, so the numbers measure how often coverage moves, not how big the catalogue is or how well it detects.
Releases
223 entries
No entries match these filters.
- November 20269
- October 202699
- September 202695
- August 202620
Articles
5 articles · updated Nov 4, 2026Where GitHub turns up in what others publish: how-tos, attack reports that name it, and incident write-ups. A row says why it is here and quotes where the article names it; the link goes to the publisher.
-
FastAPI with GitHub Actions and GHCR: Continuous Delivery Made Simple
We will guide you through the process of building and packaging your FastAPI application into a Docker image, pushing it to GitHub Container Registry (GHCR), and automating the deployment process.
2 more quotes
We’ve covered a wide range of CI topics, from the basics of setting up GitHub Actions for CI workflows, configuring triggers for running pipelines, and automating tasks using Taskfile, to building and testing FastAPI…
Our journey through the CI pipeline also included publishing test results and creating a release in the form of a Python wheel file, which was then uploaded to GitHub as part of the CI release process.
-
Enhancing GitHub Actions CI for FastAPI: Build, Test, and Publish
Create and publish a release that packages your FastAPI project into a Python wheel file and uploads it to GitHub releases for easy deployment.
2 more quotes
This continuation of our GitHub Actions CI/CD series provides a complete walkthrough of building, testing, and publishing for FastAPI applications, setting you up for seamless deployments in your continuous delivery…
Creating a Release: Package your FastAPI application as a Python wheel file , upload the release to GitHub, and prepare the application for deployment.
-
Setting Up GitHub Actions CI for FastAPI: Intro to Taskfile and Pre-Jobs
Gain valuable insights into leveraging Taskfile and pre-job configurations in GitHub Actions, along with practical advice to refine your CI pipeline and improve workflow productivity.
2 more quotes
The journey began with an introduction to GitHub Actions for Python Projects, where we delved into the concepts of Continuous Integration, Continuous Delivery, and Continuous Deployment.
What Readers Will Learn in This Post In this post, we will lay the groundwork for building a robust CI pipeline specifically tailored for a Python FastAPI application using GitHub Actions.
-
Introduction to GitHub Actions for Python Projects
Below are the key components involved in a CI/CD pipeline for Python projects: Version Control System (VCS) Tools: Git, GitHub Purpose: A central repository where code changes are stored and managed.
2 more quotes
Build Server Tools: Jenkins, Travis CI, CircleCI, GitHub Actions Purpose: Automates the build process, compiling code, and running tests.
GitHub Actions, Travis CI, and CircleCI are popular choices for Python projects.
-
Glow: The Endpoint AI Company | PixelLeak AI exposure of private developer data
Glow Labs has identified over 13,000 internal images published openly on GitHub by developers at over 300 organizations , including one of the world's largest tech companies, a frontier AI lab, a major enterprise…
2 more quotes
GitHub has an official image hosting service built directly into the site’s pull request interface.
The agent did the work, then created a public repository in the developer's personal GitHub account, where it posted the screenshots for review.
Integrates with
Explore documented product relationships, workflows and source coverage. Documentary evidence does not confirm current support or your installation's fit.
- GitHub Dependabot · GitHub · Product without a Toolchain page
| Provider product | Target product | Workflow | Evidence |
|---|---|---|---|
| Tenable One | GitHub Dependabot · Product without a Toolchain page | Import repositories, Import dependency vulnerability findings Data flows into the provider · Availability unknown |
Source 1 not confirmed |
Add the badge to your README
Maintain this project? The badge links readers straight to this page, so they can follow every release here.
 Choose a badge style and copy the code →